 Muse pdfdetach POC
The uploader demonstrates a remote code execution exploit chain against Muse, an assistant system that uses the pdfdetach utility to parse PDF attachments. The exploit leverages a path traversal vulnerability during file extraction to drop a malicious shared library and an LD_PRELOAD configuration file.
 youtu.bevideoPublished and added 30 Oct 2026🛡️ Security
- Dark Web Intelligence (@DailyDarkWeb) on X
DailyDarkWeb post summarising Anthropic Frontier Red Team research published 27 October 2026. An unreleased internal Claude research model built five attack chains: Chrome sandbox escape (V8 heap bug, CacheStorage race, FedCM use-after-free), a Safari same-origin policy bypass, data extraction from a locked Pixel 9 over USB, a Windows QUIC kernel crash (CVE-2026-33096) and zero-click Linux root via multipath TCP (CVE-2026-98432). Anthropic says all flaws are fixed, including 62 Chrome CVEs as of Chrome 156. The post notes the chains are not independently reproduced.
 x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CVE-2026-115905 is a ZIP cloaking flaw in the Rust zip crate (zip-rs/zip2), rated CVSS v4.0 10.0 and affecting versions below 9.0.5. ZipArchive reads central-directory metadata while ZipStreamReader reads local headers, so a crafted archive can pass filename inspection and then overwrite a different file during streaming extraction. Version 9.0.5 adds consistency checks, but ZipStreamReader::new leaves them off by default, and extraction is not atomic, so files can be written before an error is raised. The post covers CWE-20 and CWE-436, KEV and EPSS status, Debian status and a six-step investigation trail.
x.comadvisoryAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security  Extraction meets Distillation - cryptanalytic techniques to recover parameters from a Deep Neural Network
Extraction meets Distillation is an IACR ePrint paper (2026/2628, CSCML 2026) that combines cryptanalytic weight-direction extraction with label-based distillation to reconstruct fully connected neural networks. It adapts a ReLU extraction implementation to Leaky ReLU and proves conditional bounds for direction recovery and sign selection. On CIFAR-10 victims, reconstructed models reach 56.40% and 58.29% agreement. It separates label requests from privileged access and notes that prediction agreement does not identify parameters.
 eprint.iacr.orgpaperAdded 26 Oct 2026, published 24 Oct 2026🛡️ Security
 Introducing Clairic, a new System One class of extraction models
Clairic is Cloudflare's preview System One extraction model, hosted on Workers AI as @cf/cloudflare/clairic, with open weights planned. It reads text or images in one forward pass and returns typed values with spans, confidence, p_null, 80% intervals for estimates and forecasts. A claim-handling cascade with Clef and GLM-5.3 ran in 19.3 seconds against 61.7 for an all-LLM version.
 blog.cloudflare.comarticleAdded 29 Oct 2026, published 19 Oct 2026🧠 AI
- Saylor (@Kev96790724) on X
G-Krusch is an MIT-licensed, local-first Google Workspace hub built on Node.js 22 and SQLite WAL. It runs a 12-tool MCP server (SSE and Stdio) plus a REST bridge on port 5446 for Drive, Calendar and Gmail. It includes a 1,024-dimension hybrid Drive RAG with an embedding cascade (Ollama bge-large, then Gemini, then offline fallback) and FTS5 BM25. PDF extraction returns page citations. Tokens are kept in an AES-256-GCM vault; 30 of 30 tests pass.
x.comrepoAdded 21 Oct 2026, published 19 Oct 2026🧠 AI  Grounding Generative Verification in 3D Content
The paper introduces 3DVerifierBench, a 10-task benchmark for generative verification of 3D content. It scores accept/reject decisions, rejection explanations, and responses to controlled changes in specifications and candidates. A human study shows a 21.6-point gap to the strongest tested model, GPT-6 Astra. The authors also build a pipeline of multi-view fact extraction, controlled 3D editing and native annotations. It yields 14,126 training examples with contradiction explanations and linked counterfactuals. Verification-guided selection raises complete factual success from 26.7% to 90.0% with oracle selection over sixteen candidates, and human-guided recursive refinement satisfies all seven requirements for every input in an eight-input study.
 arxiv.orgpaperAdded 17 Oct 2026, published 15 Oct 2026🧠 AI
- Private Retrieval Augmented Generation via Random Projection
Proposes protecting the retrieval datastore in RAG systems by applying the same random projection to datastore embeddings and query embeddings. This provably preserves query-item semantic similarity while substantially mitigating data extraction attacks. Across multiple RAG architectures and datasets it beats prior differential-privacy-based methods on retrieval and generation quality, with comparable empirical privacy under strong attacks, making it a practical baseline for privacy-preserving RAG.
arxiv.orgpaperAdded 17 Oct 2026, published 15 Oct 2026🧠 AI - Private Retrieval Augmented Generation via Random Projection
Proposes applying the same random projection to both datastore embeddings and query embeddings in RAG systems. The authors claim this provably preserves query-to-item semantic similarity while substantially mitigating datastore data-extraction attacks. Across several RAG architectures and datasets it reportedly beats prior differential-privacy-based defenses on retrieval and generation quality, with comparable empirical privacy under strong attack models. It is presented as a lightweight baseline for privacy-preserving RAG.
arxiv.orgpaperAdded 17 Oct 2026, published 15 Oct 2026🛡️ Security - GhostFaceMPC: Privacy-Preserving Face Recognition with Multi-Party Computation
GhostFaceMPC is presented as the first end-to-end face recognition system that runs both the deep CNN feature extractor and the matching step under secure multi-party computation. Raw images and biometric embeddings are never exposed at any stage, from feature extraction through storage to matching. The authors contribute an MPC-friendly quantization of the GhostFaceNet model and circuit optimizations that make this practical, and they release code on GitHub. It is relevant as an example of making CNN inference feasible under cryptographic constraints.
eprint.iacr.orgpaperPublished and added 15 Oct 2026🧠 AI - GhostFaceMPC: Privacy-Preserving Face Recognition with Multi-Party Computation
GhostFaceMPC is presented as the first end-to-end face recognition system that runs a deep CNN feature extractor (GhostFaceNet) and the matching step under secure multi-party computation. Raw images and biometric embeddings are never exposed during extraction, storage or matching. The authors contribute an MPC-friendly quantization of GhostFaceNet and circuit optimizations that make the approach practical, and they release code at crypto-unict/GhostFaceMPC.
eprint.iacr.orgpaperPublished and added 15 Oct 2026🛡️ Security - gichirimaku/wp2shell-PoC
wp2shell-PoC is a Python proof-of-concept exploiting a pre-authentication RCE chain in WordPress core, combining CVE-2026-63030 (REST API batch route confusion) and CVE-2026-60137 (SQL injection in WP_Query). It demonstrates escalation from the route-desync bug through blind SQLi, customize_changeset forgery, and hook re-entry to administrator account creation and arbitrary command execution via a malicious plugin upload. The tool supports vulnerability checking, data extraction (union, error-based, blind techniques), and full shell access with or without existing admin credentials.
 github.comrepoAdded 23 Oct 2026, published 15 Oct 2026🛡️ Security
- Multi-sourced AI Tutor for Non-Native English Speaker Students
Describes a general-purpose LLM-based AI tutor for computing courses that accepts questions in Mandarin and replies bilingually, also generating glossaries of technical terms. It uses a specialized multi-source RAG pipeline with a novel question extraction mechanism to draw on diverse course materials. Evaluated on 91 Piazza posts: 83.52% answered correctly and helpfully, 76.92% of questions got high-quality translations, and 64.47% got glossaries.
arxiv.orgpaperAdded 17 Oct 2026, published 15 Oct 2026🧠 AI  ARMORY CASTLE Exploits BeyondTrust
ARMORY CASTLE (formerly UNC5221), a suspected PRC-nexus actor, exploited BeyondTrust Remote Support zero-day CVE-2026-102764 in August 2026, per Mandiant incident response. The post details the SAWFLY PHP webshell, BARECLAW SOCKS5 WebSocket tunneler, SUID root escalation, sudoers template persistence, vault credential extraction, log deletion and haproxy.conf changes. It adds YARA rules, detection ideas and patch-first remediation (BT26-05).
 cloud.google.comwriteupAdded 29 Oct 2026, published 15 Oct 2026🛡️ Security
- Robust ECDSA Threshold Signing at Scale
Presents a robust threshold ECDSA signing protocol for t ≤ (n-1)/3 corrupted signers. It batch-computes pre-processing material for fast online signing and scales to many signers, for uses such as bridging consensus between blockchains. It combines batched verifiable secret sharing (Fitzi & Hirt), randomness extraction (Beerliova-Trubiniova & Hirt), efficient share opening (Damgård & Nielsen) and Attema–Cramer zero-knowledge proofs. The authors implement it and show it is practical for large n.
eprint.iacr.orgpaperPublished and added 15 Oct 2026🛡️ Security  Anthropic says AI distillation attack defenses cut Claude extraction by 90% to 99%
News report on Anthropic's October 12, 2026 blog post saying new defenses cut reasoning-token extraction from Claude by 10x to 100x. The defenses are a two-stage extraction classifier (reported false positives under 0.1%), restrictions on reasoning transcripts, and account bans. It notes that training on full Claude Opus 4.8 reasoning transcripts scored 80.4% on SWE-bench Verified against 71.8% for summarized ones. It also covers the API changes: preserved thinking on Claude Fable 5.1 and Opus 5.5 for accounts created on or after August 31, 2026, plus Sonnet 5.5 transcripts limited to the generating organization. The article also covers alleged distillation by Zhipu (GLM-5.3) and Moonshot's Kimi, and calls for cross-industry cooperation.
 en.cryptonomist.charticlePublished and added 13 Oct 2026🧠 AI
- Anthropic says AI distillation attack defenses cut Claude extraction by 90% to 99%
Reports Anthropic's disclosure that new anti-distillation defenses cut reasoning-token extraction from Claude by 10–100x. The defenses are preserved thinking (API accounts created on or after Aug 31, 2026 can't edit prior context), per-organization transcript access limits, a two-stage extraction classifier with under 0.1% false positives, and escalating limits and bans. It also covers attacker tradecraft (hundreds of thousands of fraudulent accounts, proxy networks, stolen payment details, hidden-reasoning extraction), attribution of Zhipu's GLM-5.3 and Moonshot's Kimi traffic, and the national-security argument for cross-provider cooperation.
en.cryptonomist.charticlePublished and added 13 Oct 2026🛡️ Security  How a Misconfigured CI Workflow Became an npm Supply-Chain Compromise | Blog | Endor Labs
Endor Labs breaks down the May 11, 2026 compromise of 42 @tanstack/* npm packages (84 malicious versions) that carried valid SLSA provenance. The attacker chained a pull_request_target "Pwn Request", GitHub Actions cache poisoning across the fork/base boundary, and OIDC token extraction from Runner.Worker memory, then published directly to npm without stealing any credential. It explains why 2FA, trusted publishing, provenance and branch protection all failed, and lists mitigations: split pull_request_target workflows, treat the cache as untrusted, scope id-token: write to a publish job, pin actions to SHAs, require environment approval, use egress allowlists.
 endorlabs.comwriteupPublished and added 12 Oct 2026🛡️ Security
 US Disrupts Chinese State-Sponsored Hacking Tools
The US, alongside UK, Australian, Canadian, Japanese, New Zealand, and Spanish agencies, disrupted MicroScan and FishHub, hacking tools built by China's Integrity Technology Group and used by the state-sponsored actor Flax Typhoon (aka Ethereal Panda, Red Juliett, Storm-0919, UNC5007) against US, Japanese, Polish, and Taiwanese critical infrastructure and universities. MicroScan is a Python-based scanner with over 1,300 penetration-testing scripts targeting Apache Struts, Jenkins, WebLogic Server, WordPress, OpenSSL, and other services, delivered via a Mirai-derived IoT botnet; FishHub let operators remotely search and exfiltrate files from victim networks. The advisory also details the group's broader toolkit (SoftEther VPN for persistence, EBurst for Exchange password spraying, DC.ex for Active Directory data extraction) and the seizure of the domains used to access the tools.
 securityweek.comarticlePublished and added 9 Oct 2026🛡️ Security
- Dark Web Informer (@DarkWebInformer) on X
Infoooze is an open-source command-line OSINT reconnaissance toolkit (github.com/devxprite/infoooze) that consolidates common footprinting tasks into one CLI: username enumeration across platforms, email discovery, subdomain enumeration, port scanning, WHOIS/DNS lookups, IP/HTTP header analysis, EXIF metadata extraction, GitHub recon, and URL scanning/expansion. It automatically saves results, making it a lightweight all-in-one alternative to running several separate recon tools.
x.comrepoPublished and added 8 Oct 2026🛡️ Security - Is Memorization Context-Sensitive? Prefix-Based Extraction Beyond Isolated Prefixes
Paper measuring prefix-based training-data extraction in instruction-tuned open-weight LLMs under an empty prompt versus retrieved contexts of varying relevance (RAG), using paired item-level suffix scoring across three models. It finds extractable memorization has a context-robust core and a context-sensitive boundary: context suppresses some exposures but also enables new ones missed by prefix-only evaluation. This qualifies the claim that RAG reduces memorization risk and matters for threat-modeling deployed LLM systems.
arxiv.orgpaperAdded 9 Oct 2026, published 8 Oct 2026🛡️ Security - Is Memorization Context-Sensitive? Prefix-Based Extraction Beyond Isolated Prefixes
The paper measures whether retrieved context, as in RAG, reduces LLM memorization. It does this with paired item-level probabilistic suffix extraction: each prefix-suffix pair is scored under an empty prompt and under retrieved contexts of varying relevance, across three open-weight instruction-tuned models. Extractable memorization splits into a context-robust core and a context-sensitive boundary. Context suppresses some marginal exposures but also enables new ones that prefix-only evaluation misses, which qualifies the claim that RAG lowers memorization risk.
arxiv.orgpaperAdded 9 Oct 2026, published 8 Oct 2026🧠 AI 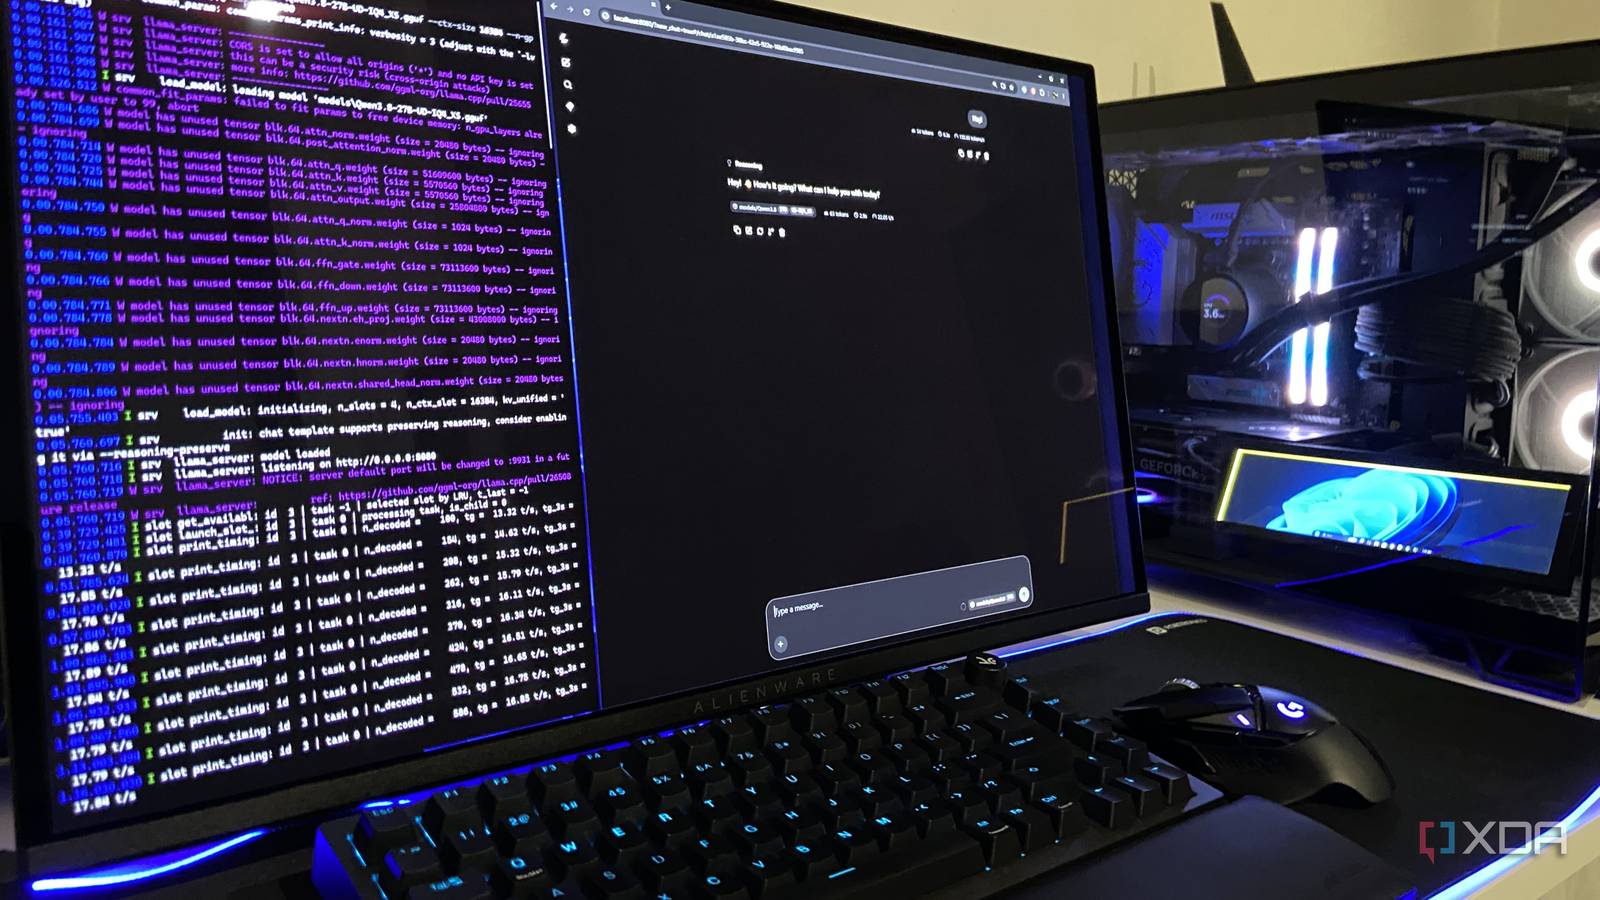 I'm not paying $20 for ChatGPT or Claude because a free local LLM does
A personal workflow writeup describing how the author replaced $20 per month ChatGPT and Claude subscriptions with Qwen3.8-27B (Unsloth UD-IQ4_XS GGUF quant, 13.3GB) run locally via llama.cpp on a 4070 Ti Super GPU with 16GB VRAM, achieving about 33.7 tokens per second at a 16K context window. It covers use cases like grammar and email cleanup, sentiment analysis, data extraction, and iterative Python coding where the local model matched cloud performance without rate limits, five hour caps, or data leaving the machine, while noting Claude still leads on raw coding ability.
 xda-developers.comarticleAdded 8 Oct 2026, published 7 Oct 2026🧠 AI
- Output Policies for Anomaly Detection with Homomorphic Encryption: Threshold Resolution, Decision Preservation, and Numerical Stability
This IACR eprint paper studies output policies for CKKS homomorphic-encryption-based anomaly detection, evaluating whether limiting released scores and decisions can hide a private detection threshold without breaking existing decisions. Across 45 plaintext and 45 CKKS experiments on three intrusion-detection datasets and autoencoder scoring models, the authors show thresholds remain estimable, quantization preserves about 99.86 percent of decisions, and a surrogate model trained on only 128 decision-only responses achieves 0.817 mean balanced accuracy at predicting decisions on new inputs, a decision-prediction model-extraction-style attack whose success depends heavily on data-splitting strategy. It argues numerical threshold leakage and decision-prediction leakage are distinct protection goals that output policies for encrypted intrusion detection systems must address separately.
eprint.iacr.orgpaperAdded 8 Oct 2026, published 5 Oct 2026🛡️ Security - DeepZero
DeepZero is an open-source orchestration engine that lets researchers define vulnerability-research pipelines declaratively in YAML, handling parallel execution (ThreadPoolExecutor), resumable/fault-tolerant state, and LLM-assessment stages via LiteLLM/Jinja2 prompts. It ships example processors for Ghidra headless decompilation, LOLDrivers.io hash exclusion filtering, PE header/driver metadata extraction, and batch Semgrep scanning, with a dedicated pipeline for BYOVD kernel driver vulnerability research. An extensibility model lets users plug in custom Python processors referenced by path in the YAML config.
github.comrepoAdded 3 Oct 2026🛡️ Security  OpenAI Banned PewDiePie Twice While He Built Ajax, an Uncensored AI That Will Run on Your PC
Decrypt reports that YouTuber PewDiePie is building Ajax, a 9-billion-parameter fine-tune of Alibaba's Qwen3.5 meant to run locally inside his self-hosted assistant app Odysseus. He describes distilling training data from OpenAI's GPT-5.6 Sol (which got his account banned twice under OpenAI's anti-distillation terms), stripping the model's built-in refusals using the open-source abliteration tool Heretic, and continuing to train it with GRPO. The piece also references an August study showing encrypted reasoning tokens from OpenAI, Anthropic and Google could be replayed and decoded from public repos, and OpenAI's late-September disruption of a reasoning-extraction campaign tied to Moonshot AI.
 decrypt.coarticlePublished and added 3 Oct 2026🧠 AI
- Guess My Weight: Profiled Side-Channel Recovery of Floating-Point Neural-Network Weights
Researchers present a profiled template attack that recovers the bit-exact IEEE-754 single-precision representation of a neural-network weight from power traces captured during inference on an embedded device. Using multivariate Gaussian templates built from Hamming-weight leakage classes and a hierarchical coarse-to-fine-to-exact search over the 32-bit floating-point space, the attack achieves 99% bit-exact recovery with 171 traces and 100% from 263 traces on a ChipWhisperer-Lite with an Arm Cortex-M4, demonstrating practical full-precision model-weight extraction from physical side-channel leakage.
arxiv.orgpaperAdded 6 Oct 2026, published 3 Oct 2026🛡️ Security - LESSER: Post-Training Data Selection with Output-Layer Gradients
LESSER is a drop-in wrapper for gradient-based post-training data selection that approximates full-parameter gradient alignment using only output-layer gradients, which can be computed with a forward pass instead of a full backward pass. It cuts feature-extraction compute by 9.7x on SFT benchmarks and 3.0x on RL benchmarks while matching the downstream performance of full-gradient selection methods, even though individual sample rankings differ, selected batches remain gradient-aligned.
arxiv.orgpaperAdded 5 Oct 2026, published 2 Oct 2026🧠 AI - CorrectGuard: Eyes-Off Correctness Estimation for Black-Box Security Guardrails
CorrectGuard is a framework for estimating whether black-box AI security guardrails made correct decisions on inputs that are inaccessible to humans (production privacy) or to the guardrail-auditing model itself, using only labeled "eyes-on" data and no internal access to the guardrail. The authors test in-context-learning, embedding, and finetuning-based correctness classifiers across 13 safety/security datasets (harmful content, jailbreaks, prompt injection, extraction) and multiple open-weight guardrails, showing up to 25-point macro-accuracy gains in error identification and improved risk-based abstention/ranking of guardrail decisions.
arxiv.orgpaperAdded 5 Oct 2026, published 2 Oct 2026🛡️ Security - CorrectGuard: Eyes-Off Correctness Estimation for Black-Box Security Guardrails
CorrectGuard is a framework for estimating how accurately black-box security guardrails (jailbreak, harmful-content, prompt-injection and extraction detectors) perform on inputs that cannot be inspected by humans or by the evaluating model itself, using an independent correctness model trained only on labeled "eyes-on" data. The authors test in-context-learning, embedding-based, and fine-tuned correctness classifiers under leave-one-dataset-out evaluation across 13 safety/security datasets and multiple open-weight guardrails, showing up to 25-point macro-accuracy gains and improved risk-coverage tradeoffs (AURC reduced from 0.33–0.44 to 0.17–0.22) for guardrail decision ranking and abstention. The work matters for anyone building auditing or eval pipelines for opaque safety classifiers without privileged access to their internals.
arxiv.orgpaperAdded 5 Oct 2026, published 2 Oct 2026🧠 AI - zzzz7788990213-ops/EvoVLM
EvoVLM searches over prompts, image preprocessing, generation budgets and answer extraction for frozen Qwen3-VL-2B-Instruct and Qwen3-VL-2B-Thinking, without fine-tuning weights. A local Qwen model ranks a catalog of typed mutations, a trusted renderer produces Python programs, and Pareto selection on accuracy and latency drives two small generations on scientific chart understanding (CharXiv subset). Recorded results on Dev128: Evolved Instruct keeps accuracy with 8.9% lower median latency, and Evolved Thinking gains 16.41 points of accuracy with 10.6% lower median latency. CPU-only replay and fail-closed evidence verification are included. The authors state the limits: small sample, overlap with the evolution set, and results tied to the recorded hardware.
github.comrepoAdded 16 Oct 2026, published 2 Oct 2026🧠 AI  OpenAI Says People Linked to China's Moonshot Tried to Copy Its AI's Hidden Reasoning
Decrypt reports OpenAI's claim that it disrupted a campaign running from July 1 to July 28. The campaign sent about 16,000 extraction requests from over 4,000 users on July 24-25, within a cluster of more than 15,000 users, and aimed to reproduce the encrypted reasoning behind model answers. OpenAI attributes a core cluster to people associated with Moonshot AI (maker of Kimi) but says it is unclear whether a single actor was behind all of it. One method copied encrypted reasoning from one conversation and asked a model to decode it in another, and OpenAI has closed that replay pathway. The article places this in the timeline of "adversarial distillation" disputes: DeepSeek, Anthropic's account of about 24,000 fraudulent accounts, the White House, xAI/Grok, and research showing provider-wide reasoning encryption keys.
decrypt.coarticlePublished and added 1 Oct 2026🧠 AI- OpenAI Says People Linked to China's Moonshot Tried to Copy Its AI's Hidden Reasoning
Decrypt reports on an OpenAI disclosure describing a campaign, starting July 1, 2026, that sent 16,000 extraction requests in a single two-day window from a cluster of over 15,000 accounts to pull out OpenAI models' encrypted "hidden reasoning" (chain-of-thought) rather than their answers. OpenAI says operators did not break encryption but manipulated model interactions to replay one conversation's encrypted reasoning for decoding in another, enabling "adversarial distillation" of a rival model's reasoning without its safety guardrails; it attributes a core cluster to individuals associated with Moonshot AI (maker of Kimi) and says it patched the replay pathway by July 28. The piece situates this alongside prior distillation disputes (DeepSeek, Anthropic's fraudulent-account claims against Chinese labs, xAI's admitted use of OpenAI outputs for Grok) and an August finding that OpenAI, Anthropic and Google each protected reasoning with a single provider-wide encryption key that attackers could coax into plaintext.
decrypt.coarticlePublished and added 1 Oct 2026🛡️ Security - Walking the Embedding Space: Datastore Extraction from Multimodal RAG
Researchers introduce ImmRAG, a black-box data extraction attack against image-returning Multimodal Retrieval-Augmented Generation (MRAG) systems, where the retrieved image itself is the model's response. Instead of malicious text prompts, ImmRAG embeds attack instructions inside an attacker-supplied image and uses relevance-weighted resampling to steer queries toward unexplored regions of the embedding space, progressively reconstructing more of the private datastore. Tested against CLIP-family retrievers across medical, document, and general-purpose scenarios, a single 2500-query run reconstructed up to 611 radiology images, 566 document scans, and 416 general images — up to 5.6x more distinct items than a non-adaptive baseline — highlighting the lack of safeguards against multimodal data leakage.
arxiv.orgpaperAdded 2 Oct 2026, published 1 Oct 2026🛡️ Security 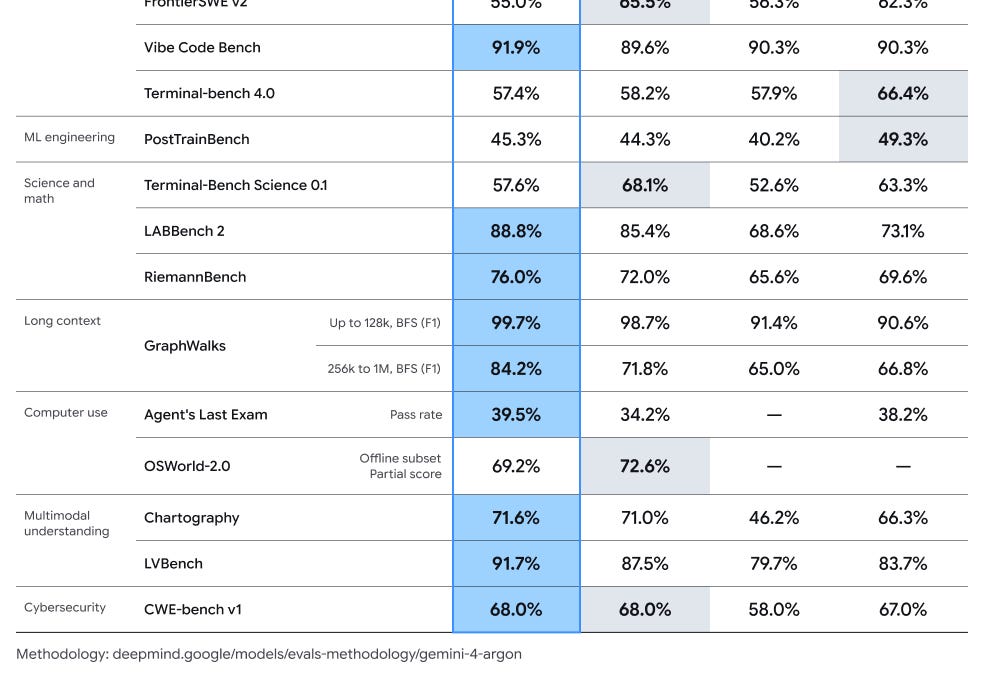 [AINews] Gemini 4 Argon: GDM’s answer to Astra/Fable, with 1M output
Latent Space's AINews digest for 9/29-9/30/2026 leads with Google DeepMind's Gemini 4 Argon, a frontier model in limited Fairwind Program cyber-defense/government preview claiming SOTA on 13 of 19 benchmarks and an industry-first 1M-token output via Long Decode Continuation, with detailed head-to-head evals against GPT-6 Astra, GPT-6.1 Sol and Claude Opus 5.5 from Artificial Analysis, Vals and Arena. It also covers other releases (Cohere Embed 5, Ideogram 4.5, GLM-5.3-Flash llama.cpp support, Solar Mini 4), research (Meta's Context Language Models, a Nature paper on superhuman Stratego AI), inference/systems news, and a safety section on hidden-reasoning-extraction attacks and GLM-5.3 cyber-capability risk.
 latent.spacearticlePublished and added 1 Oct 2026🧠 AI
- Do Defenses Against LLM Extraction Work Across Attacks? A Lifecycle Benchmark of Black-Box Model Extraction
This arXiv paper presents a reproducible benchmark that unifies evaluation of six black-box LLM extraction attacks, ten defenses, and two adaptive attacks (paraphrasing and back-translation of protected responses) under controlled query budgets and model configurations. It measures surrogate capability, fidelity to the victim model, output quality (Rep-4), and provenance-detector scores, giving a consistent basis for comparing how extraction methods and defenses interact under text-only API access. Code and artifacts are linked from the paper.
arxiv.orgpaperAdded 3 Oct 2026, published 30 Sep 2026🛡️ Security  Digital Forensics: iOS Forensics – Basics
A technical walkthrough of iOS forensic acquisition fundamentals: Apple's per-file Data Protection classes (A–D), the Before/After First Unlock (BFU/AFU) distinction and why AFU yields roughly 95% of a full dump versus almost nothing under BFU, and the iOS 18.1 72-hour auto-reboot that silently drops a seized AFU phone back to BFU. It covers extraction methods (logical backup, advanced logic, full filesystem extraction via signed agent, checkm8 bootrom exploits for iPhone X and earlier), pairing records, USB Restricted Mode's one-hour timeout, Lockdown Mode (noting it reportedly blocked FBI extraction of a seized journalist's iPhone in early 2026), Cellebrite's Inseyets/Premium/Physical Analyzer tooling and its coverage limits against A19/M5 chips with Memory Integrity Enforcement, and key forensic artifact stores (KnowledgeC, Biome, PowerLog, Photos.sqlite, chat-app SQLite/WAL/SHM files).
 hackers-arise.comarticleAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security
- Distillation Defenses Easily Break After Reinforcement Learning
This arXiv paper argues that existing defenses against distillation attacks on closed-source LLMs are evaluated under an unrealistic threat model that assumes no further training after distillation. The authors show that simple distillation attacks using data obtainable from current commercial APIs, followed by reinforcement learning, can match the reasoning gains of more sophisticated full-trace extraction attacks, breaking defenses that appeared effective when evaluated right after distillation. They conclude that any defense which leaks enough information to approximately reconstruct reasoning traces is likely ineffective, and suggest batch-level defenses as a more promising direction.
arxiv.orgpaperAdded 29 Sep 2026, published 28 Sep 2026🛡️ Security - FirmAgent: Fuzzing + LLM Agents for IoT Firmware Vulnerability Discovery (NDSS 2026)
FirmAgent is an academic research toolkit (NDSS 2026) for finding vulnerabilities in re-hosted IoT firmware web services by combining IDA-based pre-fuzzing (CFG/sink distance scoring), QEMU instrumented tracing, CFG-guided API fuzzing, and an optional LLM agent (LLMATaint.py) that consumes runtime taint traces to reason about and produce PoCs for bug classes like command injection. The pipeline is explicit about scope: it is meant for authorized, owned or re-hosted firmware (e.g. Greenhouse-style containers), and stitches together sink-scope extraction, feedback-driven fuzzing, and request-to-trace attribution before handing traces to an LLM for taint-to-PoC analysis.
github.comrepoAdded 26 Sep 2026🛡️ Security - Aray: Deterministic-First Synthesis of Benign Artifacts for YARA Validation
Aray is a deterministic-first YARA interpreter and positive-fixture synthesizer that generates benign, YARA-matching ELF/PE/generic artifacts to validate detection rules without storing or distributing live malware samples. Conventional code (not a generative model) canonicalizes rules, derives witnesses from regex/hex declarations, and performs extraction, layout, and binary serialization; an LLM is only permitted to propose constructive rule normalizations or residual-semantics judgments, never backend source or binary structure, and the pipeline supports a zero-inference execution path. Evaluated against 416 public YARA rules, it achieved 406/416 (97.6%) matches to the original upstream rule, with the design explicitly motivated by containment concerns raised by the July 2026 OpenAI–Hugging Face agent incident.
arxiv.orgpaperAdded 26 Sep 2026🛡️ Security  Mini Shai-Hulud Worm Compromises TanStack, Mistral AI, Guardrails AI & More Packages
The Hacker News details the "Mini Shai-Hulud" campaign by threat actor TeamPCP, which compromised npm and PyPI packages from TanStack, UiPath, Mistral AI, OpenSearch and Guardrails AI via a chained GitHub Actions attack (pull_request_target abuse, cache poisoning, OIDC token extraction), now tracked as CVE-2026-45321 (CVSS 9.6). The worm mints npm publish tokens directly from stolen OIDC credentials to self-propagate — the first documented case of a worm producing validly SLSA Build Level 3-attested malicious packages — and deploys an obfuscated credential stealer with IDE persistence hooks, a GitHub Actions secret-exfiltration workflow, and a dead-man's-switch that runs "rm -rf" if its rogue npm token is revoked. Over 170 packages and 400+ attacker-controlled repos have been identified across npm and PyPI, with findings credited to Aikido Security, Endor Labs, SafeDep, Socket, StepSecurity, Snyk, Wiz and Microsoft.
 thehackernews.comarticleAdded 26 Sep 2026🛡️ Security
- Let Them Steal: Trapping Large Language Model Extraction Attacks with Knowledge Honeypot
This arXiv paper introduces Knowledge Trap, a defense against model extraction attacks on commercial LLM APIs that lures attackers into querying a Honeypot Knowledge Graph (HKG) full of low-transferability knowledge via breadcrumb-guided exploration, wasting the attacker's query budget instead of blocking or perturbing outputs. Evaluated in medical and financial domains, it reduces surrogate model agreement by 6.2% on average while preserving accuracy for legitimate users, outperforming prior extraction defenses that degrade utility.
arxiv.orgpaperAdded 26 Sep 2026🛡️ Security - User Model Extraction via Belief Self-Distillation
This arXiv paper introduces Belief Self-Distillation (BSD), a technique where a frozen LLM teaches itself a compact, decodable representation of its inferred beliefs about the user, which can then be read out and rewritten back into the model's internal state. The authors show refusal behavior depends not just on the literal request but on the model's inferred user intent, and that directly editing this belief representation changes whether the model refuses a fixed request — a causal steering result with clear implications for jailbreak mechanisms and safety-conditioning defenses. They also find that independently trained LLMs converge on a similar internal geometry for representing users.
arxiv.orgpaperAdded 28 Sep 2026, published 25 Sep 2026🛡️ Security - User Model Extraction via Belief Self-Distillation
This paper introduces Belief Self-Distillation (BSD), a read-write probing framework where a frozen LLM acts as its own teacher to learn a compact representation of its implicit beliefs about the current user, which can be both decoded (read) and written back into the model's activations (write) to causally test its effect. The authors show BSD recovers user beliefs more faithfully and enables stronger interventions than matched hidden-state steering, and that changing the model's inferred user intent alters refusal decisions even when the request itself is held fixed. They also find that independently trained LLMs across different model families converge on a similar geometry for representing users, with direct implications for how safety-relevant refusal behavior depends on who the model believes it is talking to.
arxiv.orgpaperAdded 28 Sep 2026, published 25 Sep 2026🧠 AI - From Source Code to Network Profile: Automated and Traceable MUD Profile Generation for IoT Devices
AutoMUD is a source-code-driven tool that generates Manufacturer Usage Description (MUD) network access-control profiles for IoT devices by statically analyzing firmware/source code rather than relying on live traffic observation. It combines static and syntactic extraction with retrieval-grounded LLM reasoning and deterministic validation to recover rarely-exercised or conditional communication paths, link each generated rule to its source-level provenance, and record excluded findings with explicit reasons for review. Evaluated on a Linux-based repository plus a controlled semantic fault-injection campaign, it produced structurally valid, traceable MUD profiles that let analysts detect, localize and correct propagated errors.
arxiv.orgpaperAdded 28 Sep 2026, published 25 Sep 2026🛡️ Security  AI-Assisted HTTP Terminator Finds Novel HTTP Desync Techniques and Apache Zero-Day
PortSwigger researcher James Kettle built HTTP Terminator, an AI-assisted system (using Claude for extraction/test-case generation and Claude Code as an investigator agent) that ingested 138 HTTP/SMTP RFCs, split them into ~15,000 fragments, and generated 30,000 candidate HTTP desync vectors, testing them against authorized bug-bounty targets and finding ~700 vulnerable hosts. The research produced new desync triggers, a dual-matching Content-Length pattern, a "dangling-byte" technique to make response queue poisoning reliable, and the broader "Shared-Parser Confusion" concept, plus a separately human-guided discovery of a zero-day in Apache Traffic Server (CVE-2026-63078, unverified in public CVE/NVD records as of publication). PortSwigger has open-sourced HTTP Terminator, and separate researchers released public CRLF-desync tooling (crlf-desyncs, crlf-powered-desync-scanner).
thehackernews.comarticleAdded 24 Sep 2026🛡️ Security- V7 cuts costs 78% while boosting accuracy with GPT-5.6 Luna
Case study of V7 Go, an agentic workflow platform for finance and insurance. It builds a Context Graph of entities, relationships and cited evidence extracted from SharePoint and Google Drive files, with RAG fallback and an MCP server for querying and ingestion. Workflow steps are tiered across GPT-5.6 Luna (high-volume extraction), Terra and Sol (reasoning and tool use), and GPT-6 Astra (hardest graph queries). Reported results: 78% lower cost per document with Luna versus GPT-5.4 mini, tool-call error rate down from 2.7% (GPT-5.5) to 0.2% (GPT-5.6 Sol), and GPT-6 Astra at 89% versus Sol's 78% on very-hard graph-query questions. V7 also reports ~5% token savings from moving Chat Completions to the Responses API and a 69% gain over the HERB baseline. The figures are vendor and customer reported.
 openai.comarticleAdded 29 Sep 2026, published 21 Sep 2026🧠 AI
 ParaShells: Parallels Desktop Turns Appliance Install Into a Root Shell
JFrog researchers detail ParaShells, a local privilege escalation chain in Parallels Desktop 26.4.0 (build 57513) on Apple silicon that lets an unprivileged macOS user gain root. The chain combines a world-writable Unix socket for prl_disp_service, weak peer-credential-based authentication in PrlSrv_LoginLocal, and argument injection in the InstallAppliance extraction path where a crafted sVmParentPath breaks Qt's QProcess::splitCommand quoting to inject tar's --use-compress-program= flag, causing macOS tar to execute an attacker script as uid 0.
 jfrog.comwriteupPublished and added 15 Sep 2026🛡️ Security
- AD Rights Management Service (Part 2): Extraction, Offline Decryption, and the Unrotatable Key
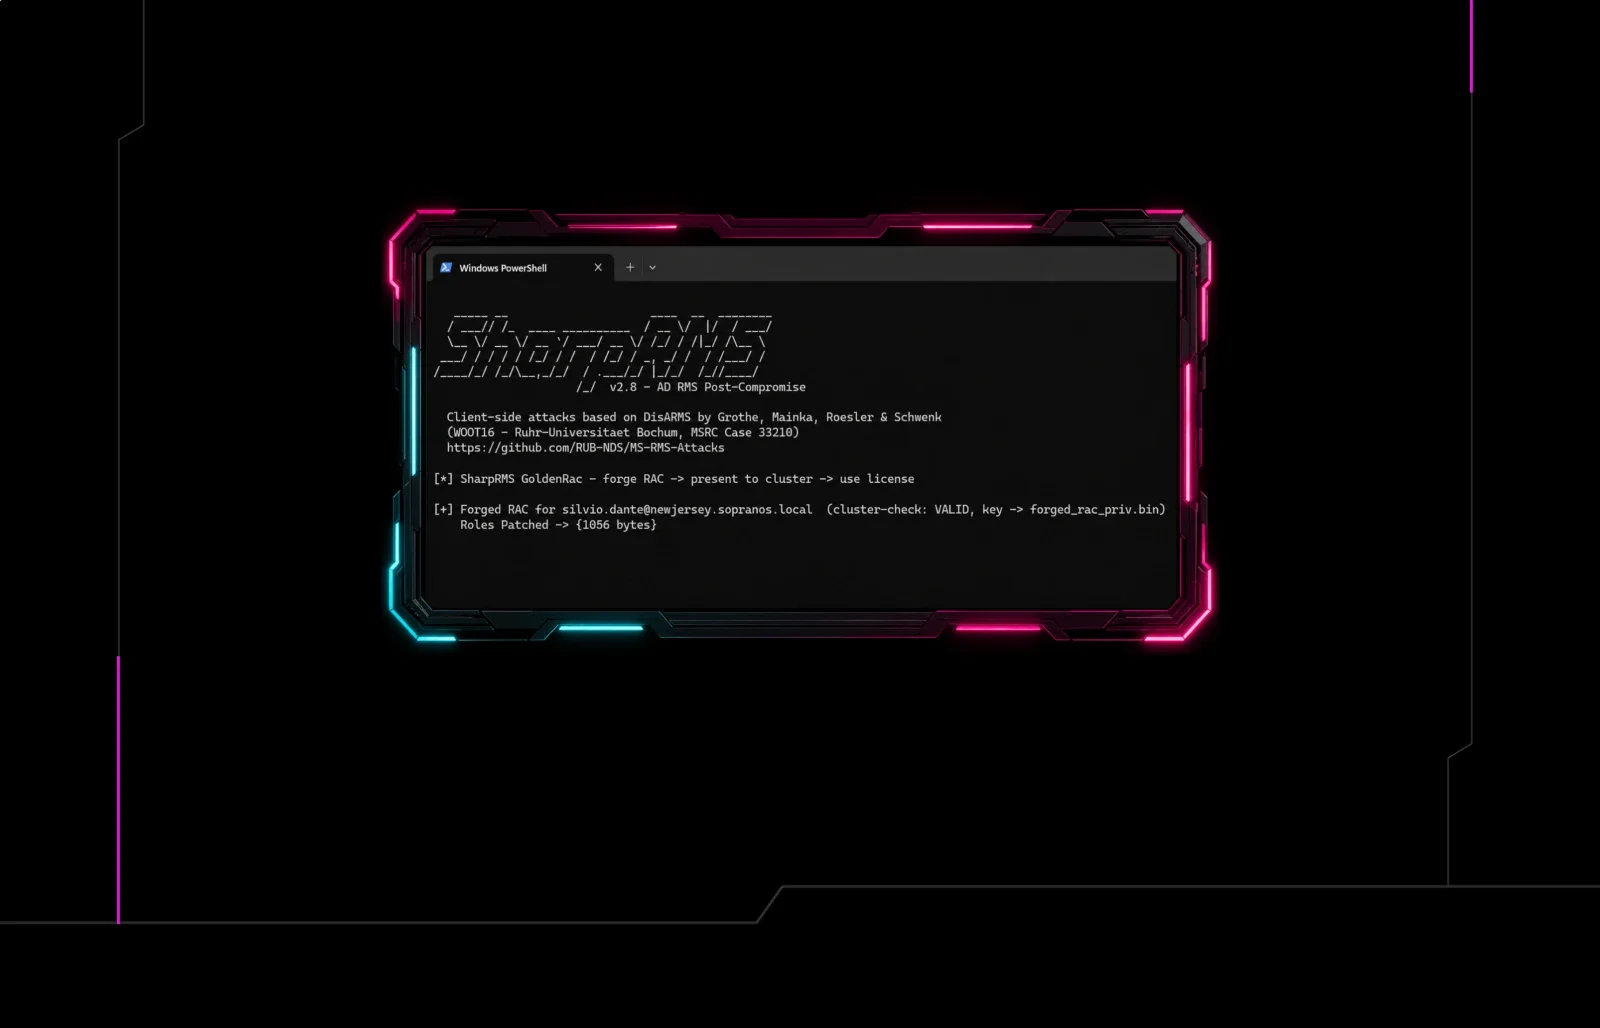
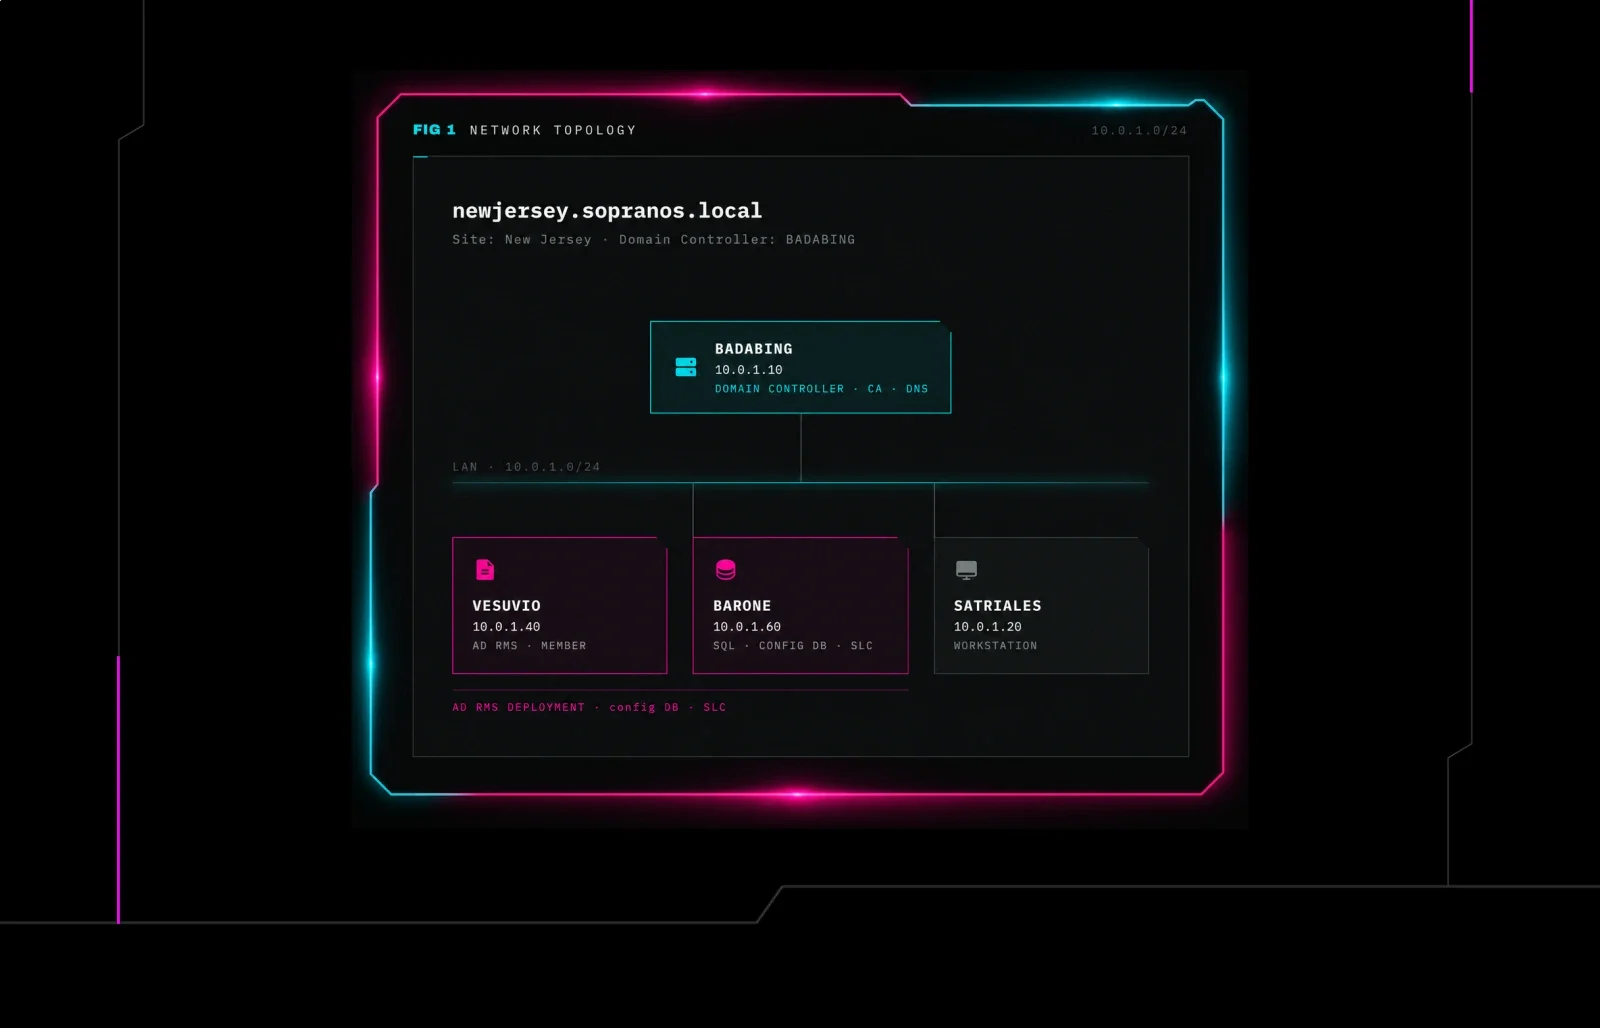
Part 2 of a Huntress series on AD RMS shows how any Service Group member can export the deployment's root SLC private key via the admin SOAP surface's Trusted Publishing Domain (TPD) operation, then use it to offline-decrypt any document the cluster has ever protected — no server contact required. The author goes further, forging XrML Rights Account Certificates signed with the stolen SLC key to trick a live AD RMS server into issuing genuine use licenses for arbitrary/impersonated identities (a "hybrid" of a Golden Ticket and Silver Ticket), and releases the SharpRMS tool that implements extraction, decryption, and RAC forgery. Because the SLC key has a 255-year certificate and no rotation mechanism, the compromise is permanent for all previously protected content, unlike KRBTGT which can be reset to invalidate forged Kerberos tickets.
 huntress.comwriteupAdded 11 Sep 2026, published 10 Sep 2026🛡️ Security
- AD Rights Management Service (Part 1): Architecture, Deprecation, and Reconnaissance
Part 1 of a Huntress research series on Active Directory Rights Management Services (AD RMS), explaining its PKI-based trust model (Server Licensor Certificate signing content keys), why it's still deployed despite Microsoft's deprecation push toward Azure Information Protection, and how to fingerprint and enumerate a cluster from an unprivileged domain account. It introduces SharpRMS, a custom C# tool that speaks the AD RMS SOAP protocol to enumerate clusters and rights-policy templates, and shows how local AD RMS Service Group membership (not Domain Admin) gates the administrative surface where the SLC private key can eventually be reached — setting up Part 2's key extraction and offline decryption.
huntress.comarticlePublished and added 8 Sep 2026🛡️ Security - kaandemir993/DarkTortilla-RAT-Telegram-Exfiltration-Payload-Extraction-Analysis
A hands-on reverse-engineering writeup dissecting a DarkTortilla RAT sample (pulled from MalwareBazaar) using Process Hacker, Binary Ninja and x64dbg. It documents the malware's credit-card theft (card_number_encrypted strings for Visa, Mastercard, Amex, Diners Club, etc.), browser credential theft via SQLite queries against Login Data files and app_bound_encrypted_key/os_crypt decryption, and three parallel exfiltration channels — a Telegram bot, SMTP mail, and FTP upload — with the C2 domain showip.net used for IP detection.
github.comrepoAdded 30 Sep 2026, published 5 Sep 2026🛡️ Security - rollroyces/py-idp
py-idp is a Python framework for intelligent document processing with a six-stage pipeline (parse, classify, extract, assess, validate, human review). It supports 23 LLM backends including OpenAI, Anthropic, Ollama, and self-hosted Nanonets-OCR2-3B. It adds Pydantic schema extraction, auto-chunking of oversized documents, an eval harness, and a review-driven policy update for confidence. It is dual-licensed AGPL-3.0 and commercial.
github.comrepoAdded 23 Oct 2026, published 31 Aug 2026🧠 AI  Potential for Remote Code Execution in Microsoft SCCM via Newly-Discovered Exploit Chain
XM Cyber researchers detail a four-stage exploit chain in Microsoft SCCM (Configuration Manager) that lets any unprivileged domain user achieve SYSTEM-level remote code execution on the primary site server: a missing authorization check on the AdminService UploadExtensionInChunks endpoint (CVE-2026-47301), a weak code-signing check that accepts any commercial certificate, a "CabSlip" Zip-Slip-style path traversal in CAB extraction giving arbitrary file write, and DLL hijacking of adsource.dll loaded by the SYSTEM-level SMS Executive service. Microsoft patched the RBAC bypass in July 2026, but the rest of the chain remains exploitable via the built-in Operations Administrator role until a full fix in ConfigMgr 2609 (October 2026); the article also gives log-based detection guidance (AdminService.log DirectoryNotFoundException/HTTP 500 patterns) and interim mitigations.
 xmcyber.comwriteupAdded 3 Sep 2026, published 13 Aug 2026🛡️ Security
- DEF CON® 34 Hacking Conference - Main Stage Talks
The official DEF CON 34 main-stage talk listing, with full abstracts and speaker bios for dozens of original research presentations spanning bootrom-to-wallet-key exploitation of the dGEN1 Ethereum phone, a privilege-escalation chain in Microsoft's Python-in-Excel Azure container (CVE-2026-45459), a novel x86 SMM hardware attack, black-box TEE key recovery on the TI OMAP-L138 via timing side channels, native-code exploitation of llama.cpp and Ollama, a CDP-based Browser-in-the-Middle AitM phishing toolkit defeating CSP/SRI, CPDLC air-traffic-control message injection via SDR, an iCloud Keychain extraction bug (CVE-2026-28860), Segmentation Fault-Oriented Programming (SFOP) for bypassing Intel CET, weaponized WMI provider post-exploitation, an autonomous AI system (HTTP Terminator) discovering novel HTTP desync attacks, quantum ML for OS fingerprinting, reverse engineering of Windows Defender's BTR.sys driver for EDR bypass, a V8 renderer RCE in Samsung Internet (CVE-2025-10891), an LLM CI build-gate bypass, a Bring-Your-Own-EDR PPL abuse technique, Amazon Locker hardware hacking, and Windows PnP USB auto-install RCE via RDP redirection.
 defcon.orgotherAdded 10 Aug 2026🛡️ Security
- npm-scan
npm-scan is a CLI supply-chain security scanner (@lateos/npm-scan) that inspects npm packages and lockfiles for behavioral attack patterns missed by npm audit/Snyk/Socket, including obfuscated payloads, credential stealers, eBPF kernel rootkits, memory-level OIDC token extraction, GitHub maintainer-account spoofing, and AI-platform-targeted key theft. It ships 23 detectors (D1-D25), validated against real campaigns like IronWorm and Miasma, and outputs SBOM (CycloneDX/SPDX) and SARIF for GitHub Security, plus a workflow to submit critical findings to CISA's VINCE with mandatory manual review. It's free (MIT) for individuals/OSS/evaluation, with paid commercial tiers ($799-$9,900/yr).
github.comrepoPublished and added 5 Aug 2026🛡️ Security - Momoko-Ayase/Senbei
Senbei is a Rust-based static unpacker for binaries protected by "CrackProof," working against both Windows PE executables and Android AArch64 shared libraries. It performs a purely static, file-local transformation (no vendor code, no key extraction service) to reverse the protection wrapper for legitimate RE, interoperability, and preservation purposes; one Android packaging variant is unwrapped using an XOR keystream the authors recovered during their own analysis.
github.comrepoAdded 4 Oct 2026, published 3 Aug 2026🛡️ Security - System Prompts Leaks
A community-maintained repository that archives leaked or extracted system prompts — the hidden instructions given to LLM chatbots before user input — captured verbatim from products including Claude/Claude Code, ChatGPT/Codex, Gemini, Grok, Cursor, Copilot, Perplexity, Meta AI, Mistral, DeepSeek, GLM, and others. It serves as a reference corpus for studying system prompt design, extraction techniques, and the system prompt leakage risk class, and is updated regularly as new prompts are exfiltrated from newer model releases.
github.comrepoAdded 3 Sep 2026, published 3 Aug 2026🛡️ Security - Semantica
Semantica is an open-source Python pipeline (pip install semantica) that ingests enterprise data and builds a queryable Context Graph and knowledge graph with deterministic (LLM-optional) reasoning, ontology management (OWL/SHACL/SKOS), and W3C PROV-O provenance for full decision auditability. It ships modules for ingestion (Databricks, Snowflake, SAP, Kafka, Git, etc.), NER/relation/event extraction, conflict detection and deduplication, Rete/Datalog/SPARQL reasoning, bi-temporal graph queries, polyglot graph storage (RDF stores and LPGs like Neo4j/Neptune), and integrations with Agno, CrewAI, LangChain, and MCP.
github.comrepoAdded 22 Sep 2026, published 1 Aug 2026🧠 AI - Beetle
Beetle is an offline-first mobile application security platform that statically analyzes Android APKs and iOS IPAs (including Flutter and React Native apps), combining decompilation, taint analysis, secret/endpoint extraction, certificate and native-binary hardening checks, and CVE enrichment with explainable 'intelligence engines' (ownership, confidence, evidence selection, finding fusion) that correlate findings into evidence-backed attack chains. It maps results to OWASP MASVS/Mobile Top 10, provides source-level navigation, and exports SARIF, CycloneDX SBOM, and PDF reports, with optional (non-scanning) AI assistance via Claude, OpenAI, Gemini, DeepSeek, or local Ollama for explaining findings.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - OSINT TikTok Extraction
A hands-on OSINT tutorial demonstrating three tools for TikTok reconnaissance: Unfurl (dfir.blog/unfurl) for decoding video IDs, usernames, and timestamps embedded in TikTok URLs; Bellingcat's tiktok-timestamp tool for extracting exact upload date/time from video links; and omar-thing.site for pulling account-level intelligence such as user ID, creation date, location, language, bio, and follower/following lists. It walks through each tool with example queries to show how public TikTok data can be turned into investigative leads.
hackers-arise.comwriteupAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security




Showing 60 of 86
Show more