- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA added two Ivanti Connect Secure vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog on 30 October 2026, citing evidence of active exploitation: CVE-2026-111357 (missing authentication for a critical function) and CVE-2026-118527 (generation of predictable numbers or identifiers). The alert restates BOD 26-04, which requires federal civilian agencies to remediate KEV-listed flaws on exposed assets and check for prior compromise. It also links the KEV nomination form.
 cisa.govadvisoryPublished and added 30 Oct 2026🛡️ Security
 CISA says max severity GitLab flaw now exploited in the wild
CVE-2026-97229 is a maximum-severity GitLab flaw in the CI/CD Regular Expression Compiler, caused by an integer overflow, that lets unauthenticated attackers run code via a crafted regular expression. CISA added it to the KEV Catalog and ordered federal agencies to patch under BOD 26-04. GitLab fixed it in CE/EE 19.4.2, 19.3.5 and 19.2.8, and Shadowserver tracks about 2,800 exposed CE instances.
 bleepingcomputer.comarticlePublished and added 30 Oct 2026🛡️ Security
 Drupal warns of critical Commerce Core flaw exploited in attacks
Drupal Commerce Core has a critical missing-authorization flaw, CVE-2026-118539, that unauthenticated attackers exploit in the wild. It affects versions 0.0.0 to 2.41 and 3.0.0 to 3.3.13. Drupal urges upgrading to 3.3.13 (or 8.x-2.41 on the older branch) and auditing orders for inconsistencies. The article also recalls CVE-2026-9082, exploited in May and added to CISA KEV, and two RCE patches (CVE-2026-108097, CVE-2026-108099).
bleepingcomputer.comarticlePublished and added 30 Oct 2026🛡️ Security Max-Severity GitLab Vulnerability Exploited Against Alpine Linux
CVE-2026-97229 is a CVSS 10 code execution flaw in Onigmo, Ruby's regular expression engine, reachable through crafted CI/CD configuration in GitLab. Attackers used it against Alpine Linux's GitLab on 20 and 21 October 2026 and failed; Alpine rebuilt the instance and found no tampering with aports or packages. Self-managed installs with their own Ruby need Ruby 3.3.13, 3.4.12 or 4.0.9, not just GitLab 19.3.6. CISA added it to KEV.
 securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security
- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 29 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities catalog on evidence of active exploitation: CVE-2026-97229, an integer overflow in GitLab CE/EE, and CVE-2026-76418, a NULL pointer dereference from an unchecked return value in Cisco Secure Firewall ASA and FTD. It restates BOD 26-04 remediation duties for federal civilian agencies and links the KEV nomination form.
cisa.govadvisoryPublished and added 29 Oct 2026🛡️ Security  A quiet week in infosec <.<
Cisco Talos Threat Source newsletter for the week of the PHP and Node.js vulnerability news cycle. It summarises NIK C2, a Go-based Windows implant that dumps credentials, streams keystrokes, deploys screen-locking ransomware and uses a victim's hijacked OpenAI API keys to analyse stolen data. It also lists weekly headlines (CISA KEV PHP bugs, Brotli flaw, Gheist GitHub token theft), Talos links and top malware hashes.
 blog.talosintelligence.comarticlePublished and added 29 Oct 2026🛡️ Security
 CISA warns of Fragnesia Linux flaw chained in PHP2Shell attacks
Fragnesia (CVE-2026-46300) is a Linux kernel XFRM ESP-in-TCP logic bug in the Dirty Frag class that gives local attackers root, with a public PoC. CISA added it to the KEV catalog and ordered federal patching under BOD 26-04. Attackers chain it with PHP2Shell (CVE-2026-109618, CVE-2026-109619) to implant PHP webshells. Dream Security tied the chain to 25 rooted servers in the US, Japan, Taiwan and South Korea.
bleepingcomputer.comarticleAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security Over 41,000 DHS Employee Records Leaked Online
A hacker using the handle Department of Peace leaked more than 41,000 US Department of Homeland Security employee records, which the hacker says came from an Okta single sign-on system. The data covers names, work emails, phone numbers, job titles, office locations and per-account system access, mostly for CBP, ICE and HSI staff plus about 1,000 CISA employees. Okta says it has no evidence of compromise. Distributed Denial of Secrets calls the dataset 'Icepick'.
securityweek.comarticlePublished and added 29 Oct 2026🛡️ Security- Chinese Hackers Quietly Used Low-Severity ESXi Logging Flaw as Zero-Day
CVE-2026-41709 is a low-severity insufficient-logging flaw in VMware ESXi that lets a logged-in administrator perform operations without audit entries. CISA added it to the KEV catalog, and CrowdStrike reported that China-nexus actor Warp Panda used it as a zero-day against US organizations, including law firms, to cut audit visibility. The article also covers exploitation of vCenter bugs CVE-2026-59309 and CVE-2026-59310 and lists the fixed ESXi builds.
securityweek.comarticlePublished and added 29 Oct 2026🛡️ Security  What is an AIBOM? AI bill of materials explained for security teams | Endor Labs
An AIBOM is a machine-readable inventory of models, datasets, dependencies, AI services, agents and MCP servers, with evidence of origin, license, integrity and evaluation. The Endor Labs explainer walks through a worked CycloneDX example for a fine-tuned support assistant. It compares CycloneDX ML-BOM, SPDX 3.x, the OWASP AIBOM project and the May 2026 CISA/G7 guidance, and lists what an AIBOM cannot show: runtime behavior and agent actions.
 endorlabs.comarticlePublished and added 29 Oct 2026🧠 AI
- What is an AIBOM? AI bill of materials explained for security teams | Endor Labs
AIBOM explainer from Endor Labs: an AI bill of materials is a machine-readable inventory of models, datasets, dependencies, AI services, agents and MCP servers, with origin, license and integrity evidence. It walks through a CycloneDX entry for a fine-tuned model, compares CycloneDX ML-BOM, SPDX 3.x, the OWASP AIBOM Generator and the May 2026 CISA/G7 minimum-elements guidance, and lists a six-step build process. It also states what an AIBOM cannot show: model safety, runtime behavior and coding-agent actions.
endorlabs.comarticlePublished and added 29 Oct 2026🛡️ Security  Leak Exposes 41,000 Homeland Security Workers–Including Undercover ICE Agents
Icepick is a leaked archive of records on more than 41,000 Department of Homeland Security employees and contractors, published by Distributed Denial of Secrets in 2026 and said to come from DHS's Okta login system. WIRED's analysis covers CBP, ICE, HSI, USCIS and CISA staff, plus over 55,000 permission groups that reference undercover programs, Palantir Falcon, PenLink, Signal and Mobile Fortify. Okta says it has no evidence of compromise.
 wired.comarticleAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security
- Hitachi Energy CoreTec Product
CISA advisory ICSA-26-302-03, republished from Hitachi Energy PSIRT 8DBD000258, covers OS command injection (CVE-2026-13162) and the Dirty Frag vulnerability (CVE-2026-43284) in Hitachi Energy CoreTec. CoreTec5 up to 3.4.0 and 5.0.0 are affected by both, and CoreTec4 up to 3.4.0 by CVE-2026-13162. The advisory was released 27 October 2026 and lists generic ICS mitigations. SSVC rates exploitation as none.
cisa.govadvisoryAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security - Hitachi Energy TRO600 series products
ICSA-26-302-02 is a CISA republication of Hitachi Energy PSIRT advisory 8DBD000224 on the TRO600 series. It covers CVE-2026-10756 and CVE-2026-106087, which allow remote code execution and disclosure of sensitive information. Affected versions are TRO600 up to 9.2.1.6 and 9.1.1.0, plus 9.2.2.1 and 9.1.2.0. The page gives no per-CVE detail or CVSS scores, only general ICS hardening advice. Released 27 October 2026.
cisa.govadvisoryAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security - CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 28 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities Catalog on evidence of active exploitation: CVE-2026-41709 (Broadcom VMware ESX insufficient logging) and CVE-2026-46300 (Linux kernel missing variable initialization). It restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise. It also links the KEV nomination form.
cisa.govadvisoryAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security  Christiaan Stoudt (@cstoudt) on X
Thread on CVE-2026-97631, a critical (9.5) flaw in TianoCore EDK II UEFI firmware, found by Alex Matrosov and Dan Holmes-Mitra. It is exploitable only while a machine is PXE network booting and the attacker sends an oversized ICMP error from the same network. Code execution also needs the exact firmware build, and Secure Boot does not help. The fix landed in EDK II main on 15 October but is not in a stable release. No known exploitation, and not in CISA KEV.
 x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security
 Long-Hidden Flaws Patched in EPICS Research Facility Control Software
Four vulnerabilities in EPICS Base 7.0.10 and earlier, the control-system toolkit used at ITER and the Advanced Photon Source, were disclosed by CISA. CVE-2026-114595 (CVSS 9.8) is an integer overflow that could allow remote code execution, though only an out-of-bounds heap write and crash were demonstrated. All flaws sit in Channel Access and pvAccess handling (TCP 5064 and 5075), need no authentication, and are fixed in 7.0.11.
securityweek.comarticlePublished and added 28 Oct 2026🛡️ Security CISA Warns of Node2Shell Exploitation as Honeypots Log Attack Attempts
CVE-2026-111497 (Node2Shell, also HTTP2Shell and Broccoli2Shell) is an out-of-bounds write in the Brotli decoder, affecting versions 1.0.3 through 1.2.0. CISA added it to the KEV catalog on 27 October 2026 with a federal deadline of 10 November. Previdian and ELLIO logged exploitation attempts; ELLIO found the observed exploit broken but achieved code execution itself, and Broadcom's VMware SDDC Manager patches are pending.
securityweek.comarticlePublished and added 28 Oct 2026🛡️ Security- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 27 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities (KEV) Catalog on evidence of active exploitation: CVE-2026-48356, an unrestricted upload of a dangerous file type in Adobe Commerce and Magento, and CVE-2026-111497, an unchecked return value in Google Brotli. It restates BOD 26-04, which makes federal civilian agencies prioritise KEV flaws on exposed assets and check for prior compromise. No technical detail or IOCs are given.
cisa.govadvisoryAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security  This is Fine: What NetScaler Zero-Days Tell Us About the New Normal
This SecurityWeek commentary covers the September 2026 Citrix NetScaler ADC and Gateway zero-days, exploited from mid-month and patched on 27 September as unauthenticated RCE flaws CVE-2026-88771 through CVE-2026-88778. The author argues the fast response shows stronger defence. Cited evidence: Citrix disclosure time fell from about 40 days to 17 in 2026 after it set up a NetScaler CNA, and CISA made a rare Sunday KEV addition.
securityweek.comarticlePublished and added 27 Oct 2026🛡️ Security Maritime Coalition Launches Free Vulnerability Database for Ship and Port Systems
Blue Initiative is a free public vulnerability database for maritime IT and OT, built by Cydome, ClassNK, Bureau Veritas, MTS-ISAC and Rakuten Maritime. It holds nearly 30,000 entries, over 2,000 rated critical by CVSS and more than 580 known exploited. Only 37 affect ship and port products. Most entries are pulled from CISA ICS advisories and the KEV catalog and mapped to maritime systems.
securityweek.comarticlePublished and added 27 Oct 2026🛡️ Security- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA added two PHP vulnerabilities to its Known Exploited Vulnerabilities Catalog on 26 October 2026: CVE-2026-109618 (memory corruption) and CVE-2026-109619 (stale internal request state). It also updated its PHP alert on critical vulnerabilities requiring immediate patching. The alert restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise.
cisa.govadvisoryAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security - Mitsubishi Electric and Mitsubishi Electric Iconics Digital Solutions GENESIS, GENESIS64, ICONICS Suite, Hyper Historian, AnalytiX, MobileHMI, IoTWorX, MC Works64, GENESIS32 and BizViz
CISA advisory ICSA-26-300-02 covers four vulnerabilities in Mitsubishi Electric and Mitsubishi Electric Iconics Digital Solutions GENESIS64, ICONICS Suite, Hyper Historian, AnalytiX, MobileHMI, IoTWorX, MC Works64, GENESIS32 and BizViz. CVE-2023-4863 (CWE-787 out-of-bounds write) allows code execution; CVE-2026-16436 and CVE-2026-16437 allow authentication bypass; CVE-2026-16438 allows arbitrary operations. Fixes are 10.97.3, 10.98 and GENESIS 11.04. MC Works64, GENESIS32 and BizViz are affected in all versions, and MC Works64 has no fix planned. Mitigations include removing the ClientChallengeTable.dat or SecurityChallenges.dat file contents. The fetched text was truncated, so later content is not covered.
cisa.govadvisoryAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security - EPICS Base
CISA ICS advisory ICSA-26-300-01 (October 27, 2026) covers EPICS Base release 7.0.10 and earlier, with CVE-2026-114595 through CVE-2026-114598. Flaws include integer overflow, length parameter inconsistency and type confusion, allowing denial of service, memory corruption, information disclosure or remote code execution (CVSS v3.1 9.8). The fix is EPICS Base 7.0.11, with patches in epics-base and pvDataCPP pull requests.
cisa.govadvisoryAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security - CISA Publishes Significant Updates to ScubaGear and ScubaGoggles
ScubaGear v2.0 and ScubaGoggles v1.1.0 are CISA's updated SCuBA assessment tools for Microsoft 365 and Google Workspace secure configuration baselines. ScubaGear now uses direct REST API calls, adds Power BI coverage, a consolidated Security Suite baseline and app severity scoring. ScubaGoggles adds a GUI, Policy API integration and Gemini controls. The release supports BOD 25-01 compliance.
cisa.govarticleAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security  Stolen AI Reasoning Could Help China Build Cheaper Rivals
Compaction Smuggling is an attack found by Xint that bypassed OpenAI's August 2026 mitigations against stealing reasoning traces from proprietary LLM APIs. It encodes one model's reasoning inside a compaction and replays it to another model (for example gpt-4.1 or gpt-4o), which outputs it verbatim. OpenAI fixed it and paid a $6,000 bounty on 23 October 2026. The article ties it to distillation by Chinese labs, citing a September CISA warning.
securityweek.comarticlePublished and added 26 Oct 2026🛡️ Security- PHP2Shell Exploitation Moves From Probes to Working Shells
PHP2Shell exploitation (CVE-2026-109618, CVE-2026-109619) reached working shells on 24 October 2026, when Perplexity researcher Adel Karimi's honeypots (PHP 8.4.26, Apache mod_php, single worker) logged 35 shells across three servers. Attackers used a four-stage HTTP chain: memory exhaustion, memory leak, then shell command execution, matching a public PoC. No second-stage payload was seen, and CISA had not added the flaws to KEV as of 26 October.
securityweek.comarticlePublished and added 26 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge Weekly CVE Rundown #007 covers six CVEs from 19 to 24 October 2026: SiteGuard command injection (CVE-2026-106931), DB-GPT (CVE-2026-77932), Siemens Software Center DLL side-loading (CVE-2026-110936), Cisco Expressway (CVE-2026-76466), Node.js Brotli (CVE-2026-111497) and Arista VeloCloud (CVE-2026-114625). Each entry gives defender actions, fixed versions, exploitation status and primary-source links. Updated 25 October 2026 with CISA KEV and EPSS findings.
x.comarticleAdded 27 Oct 2026, published 25 Oct 2026🛡️ Security - CISA: Critical Vulnerabilities in PHP Require Immediate Patching
CISA alert on CVE-2026-109618 and CVE-2026-109619 ("php2shell"), unauthenticated remote code execution flaws affecting PHP installations serving web requests, including mod_php, PHP-FPM, php-cgi, FrankenPHP and LiteSpeed. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Updated 23 October 2026 with a Sigma rule, partner advisories (NSA, NCSC-UK, ASD ACSC, NCSC-NL, NCSC-NZ, Cyber Centre) and guidance to inventory PHP, patch internet-facing systems first, and watch for PHP workers spawning shells. No in-the-wild exploitation had been observed.
cisa.govadvisoryAdded 24 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CVE-2026-111497 is an out-of-bounds write in the Brotli decoder bundled with Node.js (CWE-787, CWE-252), rated CVSS v4.0 9.2 by the Google CNA and High by the Node.js project. Fixes are Node 22.23.4, 24.22.1 and 26.12.1, and 24.22.1 still labels Brotli 1.2.0 because the fix was cherry-picked. The post gives a SOC trail from input to worker, with remediation and verification steps. It notes no KEV match, CISA SSVC exploitation none, and only unverified public lab claims.
x.comadvisoryAdded 26 Oct 2026, published 23 Oct 2026🛡️ Security - ENISA Technical Advisory for Software Bill of Materials
ENISA Technical Advisory for Software Bill of Materials (October 2026, TLP:CLEAR) is non-mandatory guidance for organisations, especially SMEs, starting SBOM adoption. It covers SBOM data models (CycloneDX, SPDX), a mapping of BSI TR-03183-2 fields to CISA minimum elements, lifecycle and CI/CD integration, an SBOM threat model, and security recommendations. It supports Cyber Resilience Act obligations but is not a legal interpretation.
 enisa.europa.euadvisoryAdded 23 Oct 2026🛡️ Security
 PHP2Shell Exploitation Started Days Before Patches
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) is a pair of critical PHP remote code execution flaws. Amazon saw the first exploitation on 17 October 2026, four days before patches on 21 October, and Cloudflare logged millions of attempts after disclosure. Censys, VulnCheck and VirusTotal counted over 1 million unpatched PHP hosts, and CISA urged updating to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35.
securityweek.comarticlePublished and added 22 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CyberForge CVE of the Day #084 analyses CVE-2026-76466, a CVSS 9.8 flaw in clustered Cisco Expressway-C and Expressway-E. Persistent database cookies and weak client-certificate validation allow root OS command execution over the network. The fix is X15.5.20 (X14 and earlier must migrate), with no workaround. It adds a per-peer SOC investigation trail, reachability checks and exposure status from CISA SSVC, KEV and EPSS.
x.comadvisoryAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CVE-2026-110936 is an uncontrolled DLL search path flaw (CWE-427) in Siemens Software Center below V4.0.9.8, listed in CISA KEV on 20 October 2026. The post covers CVSS v4.0 8.4 and v3.1 6.7, Siemens' Romulus ClickFix campaign indicators (IPs, domain, hashes, file leads) and a six-step SOC trail using Sysmon, EDR and network records. It separates delivery from DLL load and from compromise.
x.comarticleAdded 24 Oct 2026, published 21 Oct 2026🛡️ Security - #StopRansomware: SafePay Ransomware (AA26-293A)
CISA advisory AA26-293A (20 October 2026) details SafePay ransomware, active since August 2024 with at least 600 victims across critical infrastructure. It covers initial access via Mullvad VPN IPs, phished profiles and edge-device CVEs, LOTL lateral movement with PsExec, WinRM and RDP, exfiltration with RClone and WinSCP, and ChaCha20/RSA encryption. It lists IOCs, MITRE ATT&CK mappings, incident response steps and mitigations.
cisa.govadvisoryAdded 21 Oct 2026🛡️ Security  Threat Brief: Active Exploitation of PAN-OS CVE-2026-0257 (Updated Oct 20)
Unit 42 threat brief on active exploitation of CVE-2026-0257, a PAN-OS GlobalProtect authentication bypass added to CISA KEV on May 13, 2026. It lists IP addresses, host IDs and PoC-derived client values to hunt in GlobalProtect logs. The October 2026 updates cover Qilin and Inc ransomware operators, MFA bypass, pivots to vCenter and ESXi with offline VMDK credential dumping, and management interface exposure on ports 4443 and 3879.
 unit42.paloaltonetworks.comadvisoryAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security
 US Agencies Detail Incident Response Practices for Rogue AI Agents
SecurityWeek summarizes the NIST, NSA and CISA report "Key Practices for Incident Readiness and Response in Super Intelligence Training and Evaluation". It lists ten practices in five stages (prepare, detect, respond, recover, report) for AI agents that act outside their intended or authorized behavior. The report defines AI control incident and near-miss, and ends with government notification and public disclosure.
securityweek.comarticlePublished and added 20 Oct 2026🛡️ Security There's only so much code: the rise in vulnerability numbers
Cisco Talos analysis of why Microsoft Patch Tuesday advisories rose from about 100 a month before June 2026 to 975 in September and 1,415 in October, as frontier models such as Mythos mine old code. CVEs grew 105% year over year while CISA KEV additions grew 37%, and only three September advisories were exploited in the wild. It covers pressure on 90-day coordinated disclosure and open-source maintainers, the format string bug-class precedent, and defender advice.
blog.talosintelligence.comarticlePublished and added 20 Oct 2026🛡️ Security The US orders every civilian agency to rip out DeepSeek, even tools built on it
DHS Exclusion and Removal Order #2026-01, signed by Secretary Markwayne Mullin and dated 24 July 2026, bars every federal civilian agency from buying or running DeepSeek products and third-party tools built on DeepSeek implementations. The order does not list affected products or address DeepSeek models hosted by US firms. Agencies have 60 days to request exceptions through CISA, and military and intelligence systems are excluded.
 madrobot.blogarticleAdded 20 Oct 2026, published 19 Oct 2026🧠 AI
- The US orders every civilian agency to rip out DeepSeek, even tools built on it
DHS Exclusion and Removal Order 2026-01, signed by Secretary Markwayne Mullin on 24 July 2026 and noticed in the Federal Register on 20 October 2026 (docket DHS-2026-0628), bars civilian agencies from buying or running DeepSeek products and third-party products built on DeepSeek. Agencies have 60 days to request exceptions through CISA and must meanwhile monitor traffic, increase logging and add data-exfiltration controls. Military and intelligence national security systems are excluded.
madrobot.blogarticleAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security  Exploited Fortinet Bug Linked to Stealthy FortiGate Implant in Telecom Hack
UNC5820 (tracked by Palo Alto Networks as CL-STA-0954) breached a telecom in September 2024 using FortiManager flaw CVE-2024-47575 (FortiJump) and path traversal CVE-2025-61624, then deployed PeerStitch, a memory-resident ARM64 FortiGate implant. PeerStitch patches FortiOS log and IKE/IPsec daemons to build a covert bridge without listening ports. The actor also impersonated FortiManager over FGFM, using CVE-2024-26008. CISA added CVE-2025-61624 to KEV.
securityweek.comarticlePublished and added 19 Oct 2026🛡️ Security- Dark Web Intelligence (@DailyDarkWeb) on X
Plex2Shell is a chain of four Plex Media Server flaws (CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656) that a researcher says ends in unauthenticated RCE on servers older than 1.43.3.10861. A write-up and PoC were published on 16 October 2026. CISA advisory VA-26-266-01 scores the individual CVEs 4.3 to 7.2, and they are not in CISA KEV. The post advises updating, avoiding exposure of port 32400, and checking for unknown child processes and new files in the Codecs folder.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
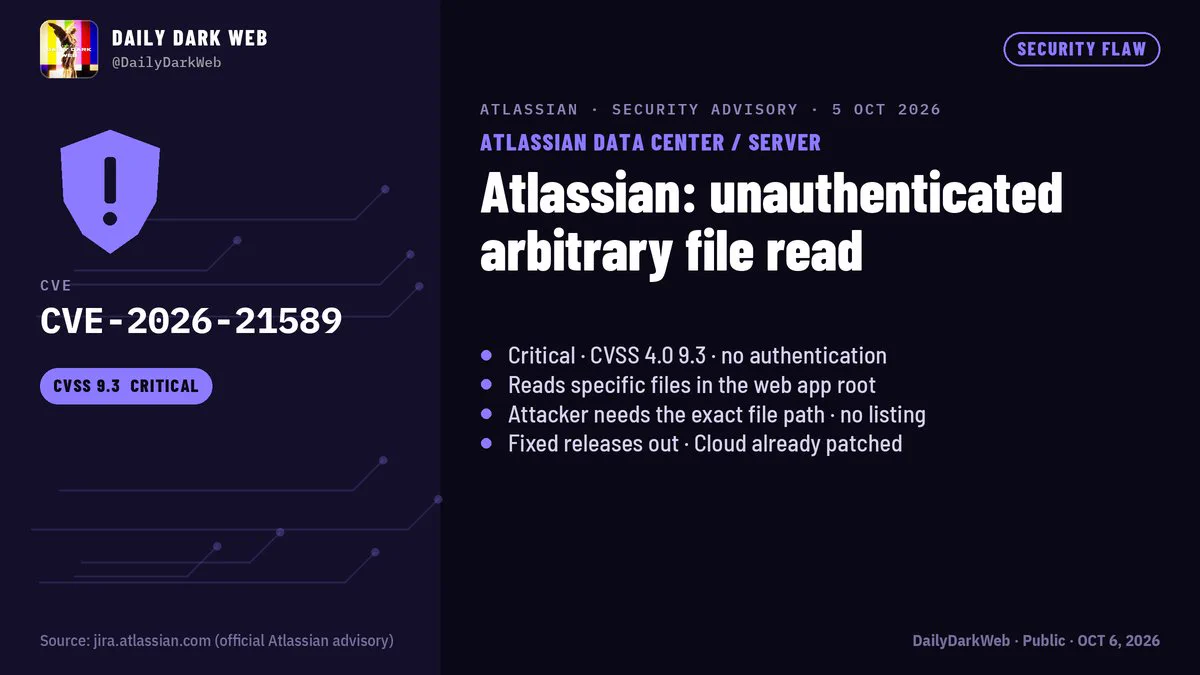
DailyDarkWeb update on CVE-2026-21589, a pre-auth file-read flaw in Atlassian Data Center products. The CVE record was rejected on 16 October 2026 with a generic reason and no replacement ID, but Atlassian's advisory (CVSS v4.0 9.3, Critical) and the CISA KEV listing (added 15 October, federal due date 18 October) remain. The analyst note says to keep patching to the fixed versions and track versions, not only the CVE ID.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security  Frequently Asked Questions About the BeyondTrust Remote Support Arbitrary File Upload (CVE-2026-102764)
CVE-2026-102764 is an arbitrary file upload in BeyondTrust Remote Support (formerly Bomgar) caused by internal appliance components not validating message origin. Mandiant found it exploited as a zero-day in late August 2026. BeyondTrust disclosed it on 15 October 2026 and CISA added it to KEV on 16 October 2026. The FAQ covers the web shell, root escalation, credential theft, persistence, patching and compromise checks.
 watchtowr.comadvisoryAdded 30 Oct 2026, published 16 Oct 2026🛡️ Security
 BeyondTrust Remote Support Arbitrary File Upload (CVE-2026-102764)
CVE-2026-102764 is a CVSS 9.8 unauthenticated arbitrary file upload flaw in BeyondTrust Remote Support (formerly Bomgar) and Privileged Remote Access. Internal messaging components do not verify message origin, so remote attackers can plant files the appliance would reject. BeyondTrust disclosed it on 15 October 2026 with patch BT26-05, and CISA added it to KEV on 16 October 2026. The page lists log files to review and hardening steps.
watchtowr.comadvisoryAdded 30 Oct 2026, published 16 Oct 2026🛡️ Security U.S. jobs data challenges fears about the future of artificial intelligence
Reports Stephen Messer's October 2026 essay arguing that US unemployment (4.3–4.5% through 2025–2026) and studies from Anthropic economists, PwC and a Danish dataset show no mass AI job destruction. It also covers Yann LeCun's rejection of LLMs as a route to human-level intelligence and open-weight competition, notably Moonshot's Kimi K2 to K3 and Harvey's Tenet model post-trained on Kimi K3 (benchmark 11% to 19.7%, inference cost under a quarter). It closes with the September 2026 FBI/NSA/CISA advisory on Chinese distillation campaigns against US models.
 en.cryptonomist.charticlePublished and added 16 Oct 2026🧠 AI
- lee1981 (@lee1981b) on X
Daily CVE digest on CVE-2026-76519, a CVSS 9.8 relative path traversal (CWE-23) in Cisco Secure Email Gateway's AMP File Reputation attachment processing. A crafted attachment gives unauthenticated arbitrary file writes and root command execution, and Cisco PSIRT reports active exploitation. The CVE is in CISA KEV. It lists the applicability conditions (File Reputation assigned to a policy and Content Scanner Tools earlier than 25.3.0.5525) and the fixes (scanner 25.3.0.5525, AsyncOS 15.5.5-014 and 16.5.0-780). It also covers evidence preservation, reading Cisco's System Security scan outcomes, mail/AMP log correlation, and deployment-specific recovery including cluster-key exposure.
x.comadvisoryAdded 18 Oct 2026, published 15 Oct 2026🛡️ Security  Palo Alto Networks Patches PAN-OS Zero-Day Exploited for Remote Code Execution
Palo Alto Networks patched CVE-2026-0322, a high-severity zero-day in the PAN-OS management interface that lets an authenticated attacker with network access run arbitrary code as root. It affects PA-Series, VM-Series and Panorama with no special configuration needed, and "very limited" exploitation has been seen. The vendor published a few IP-based IoCs, CISA added the flaw to KEV with an October 17 deadline, and a dozen other medium/low advisories were released the same day.
securityweek.comarticlePublished and added 15 Oct 2026🛡️ Security Cisco Warns of Exploited Secure Email Gateway Vulnerability
Cisco warned that CVE-2026-76519 (CVSS 9.8), an unauthenticated arbitrary file write in the Advanced Malware Protection feature of Secure Email Gateway, is exploited in the wild. Crafted email attachments can lead to root command execution when file reputation is enabled and Content Scanner Tools is older than 25.3.0.5525. Fixes shipped September 14 in AsyncOS 15.5.5-014 and 16.5.0-780. Cisco published IoCs, advises rebuilding virtual appliances and rotating credentials, and CISA added the flaw to KEV. It is the second exploited SEG bug since mid-September, after CVE-2026-76461.
securityweek.comarticlePublished and added 15 Oct 2026🛡️ Security Critical GitLab RCE Lets Unauthenticated Attackers Execute Code on Servers (CVE-2026-97229)
Orca Security analysis of CVE-2026-97229, a CVSS 10.0 flaw in GitLab CE/EE. An integer overflow (CWE-190) in the CI/CD regular expression compiler gives memory corruption and code execution as the git user. It is triggered by a crafted regex in .gitlab-ci.yml combined with a UTF-8 repository path, with no authentication needed on instances that allow public project creation or self-registration. Lists affected branches (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2), the absence of a workaround, interim mitigations, and a Rapid7 PoC against GitLab CE 19.4.1 with ASLR on. Notes a prior max-severity GitLab bug (CVE-2026-85706) was probed in the wild within hours and later added to CISA KEV.
 orca.securityadvisoryPublished and added 14 Oct 2026🛡️ Security
 ICS Patch Tuesday: Siemens Issues 17 Advisories, Rockwell Fixes ArmorBlock Takeover Flaw
Roundup of ICS Patch Tuesday advisories. Siemens published 17 advisories, including critical flaws in Simatic S7-1500 CPUs (400+ flaws in the GNU/Linux subsystem), Industrial Edge and Ruggedcom Crossbow SAC. Rockwell fixed a critical 1732E ArmorBlock flaw that lets an unauthenticated attacker change the web server password and take over the admin account, plus a DoS bug. Also covered: two high-severity Schneider Electric advisories (Pro-Face STW6000/Harmony STW6 and Sage RTUs), CISA and CERT@VDE advisories, and other vendor advisories since the last Patch Tuesday. ABB's dynovaPRO credential-reset bypass came with 26 password change events across 9 customers that may indicate reconnaissance.
securityweek.comarticlePublished and added 14 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
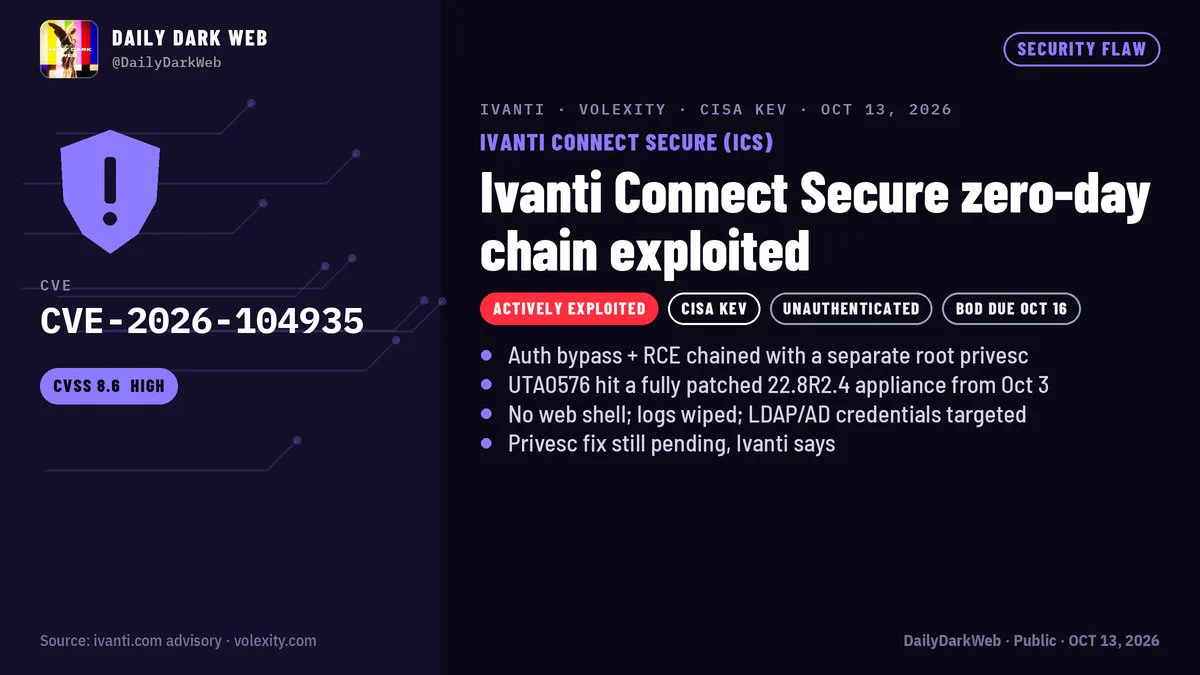
Defender guide for CVE-2026-104935, an authentication-bypass-by-spoofing flaw (CWE-290) in Ivanti Connect Secure that allows unauthenticated command execution. It is confirmed exploited and CISA KEV-listed, with a CNA CVSS 8.6. It covers the fixed-release matrix (25.1.1.2, 22.8R2.5, 25.1.3.x), platform and cluster migration limits, and Volexity's UTA0576 indicators and YARA rules. It also gives a six-step SOC workflow (scope, preserve, hunt, correlate identity, remediate, verify). It stresses that a clean ICT result cannot clear memory-only activity and that LDAP, LAPS and BitLocker exposure belongs to one observed chain.
x.comthreadAdded 16 Oct 2026, published 14 Oct 2026🛡️ Security - ThreatWire (@ThreatWire_) on X
ThreatWire post on CVE-2026-97229, an integer overflow in the GitLab CI/CD regex compiler. GitLab rates it CVSS 3.1 10.0 and says it can allow unauthenticated code execution under certain conditions, in both CE and EE. Fixes are in 19.2.8, 19.3.5 and 19.4.2 (not 19.3.4), released Oct 12; GitLab-hosted instances are already patched. The post credits joaxcar via HackerOne and says a Rapid7 researcher published a lab PoC on GitHub, which ThreatWire has not run or verified. It also says the CVE is not in CISA KEV and has no known exploitation.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026🛡️ Security  Microsoft Patches Record 1,413 Vulnerabilities, Including Exploited Windows Zero-Day
SecurityWeek reports Microsoft's October 2026 Patch Tuesday fixed a record 1,413 CVEs (1,102 in Windows, 134 Office, 36 SharePoint), more than all of 2025, with the surge attributed largely to AI-driven discovery. The exploited zero-day CVE-2026-96951 is a Windows shell Mark of the Web security feature bypass (CVSS 8.8), added to CISA KEV with an October 16 deadline. Two flaws were publicly disclosed: CVE-2026-108398 (WDAC bypass) and CVE-2026-92707 (MessagePack-CSharp DoS), and Microsoft introduced 'risk cohorts' for patch prioritization.
securityweek.comarticlePublished and added 14 Oct 2026🛡️ Security- Dark Web Intelligence (@DailyDarkWeb) on X
Summary of SAP's October 13, 2026 Security Patch Day (16 new notes, 4 GitHub advisories). It leads with CVE-2026-89111, a CVSS 10.0 OAuth2 SSRF in SAP Cloud SDK for Python before 0.45.2, where an attacker-controlled tenant_subdomain redirects token requests and exfiltrates client credentials. It also lists three other critical flaws: broken access control in NetWeaver Visual Composer, code injection in S/4HANA substitution/validation rules, and a missing authorization check in the Manufacturing Integration and Intelligence (XMII) Configuration Service. It notes that none are in CISA KEV and SAP reports no in-the-wild exploitation.
x.comadvisoryAdded 15 Oct 2026, published 13 Oct 2026🛡️ Security  Part 2 – Cybersecurity journeys: What even is this job?
Part 2 of the AWS Security Blog's cybersecurity careers series. It profiles three people in less-publicized security roles: Jason Lane, who works backward from a vulnerability research goal and now measures risk across about a million Amazon applications. Jason Goodman moved from customer service through insider threat, adversarial detection and application security. Harshvardhan Chunawala advises startups and has worked on lunar rover operations and satellite incident response. It closes with pointers to the NICE Workforce Framework, CyberSeek, AWS Skill Builder and CISA resources for exploring roles.
 aws.amazon.comarticlePublished and added 13 Oct 2026🛡️ Security
- Dark Web Intelligence (@DailyDarkWeb) on X
Social post summarizing Volexity's research on an Ivanti Connect Secure (ICS) zero-day chain, CVE-2026-104935. The chain pairs an auth bypass and a race-condition RCE with a separate privilege-escalation bug for root. Actor UTA0576 used it from Oct 3, 2026 against a fully patched 22.8R2.4 appliance, leaving no backdoor or web shell and deleting log entries. Post-exploitation included LDAP/AD credential theft, LAPS and BitLocker key searches, password spraying and packet capture. CISA added it to KEV with a due date of Oct 16. A clean Integrity Checker result does not rule out compromise because the chain patches code in memory only, so memory and network forensics are needed. The hunting lead is heavy requests to /dana-na/auth/url_default/welcome.cgi with a mismatched X-DSCGI-PATH header.
x.comthreadPublished and added 13 Oct 2026🛡️ Security  Ivanti Connect Secure zero-day exploited in the wild (CVE-2026-104935)
Rapid7 emergency-response analysis of CVE-2026-104935, a CVSS 8.6 authentication bypass by spoofing (CWE-290) in Ivanti Connect Secure that allows unauthenticated remote command execution. It was exploited as a zero-day against a limited number of customers, added to CISA KEV on disclosure day, and Volexity observed it chained with a still-unpatched privilege escalation flaw. Part of the fix shipped in 25.1.3.0 in July 2026, with backports to other supported versions pending. Rapid7 advises emergency patching outside normal cycles and hunting for compromise using Volexity's IOCs, since Ivanti has no reliable ones.
 rapid7.comadvisoryPublished and added 13 Oct 2026🛡️ Security
 Frequently Asked Questions About the Ivanti Connect Secure Authentication Bypass by Spoofing (CVE-2026-104935)
CVE-2026-104935 is an authentication bypass by spoofing in Ivanti Connect Secure. A remote attacker can forge identity signals and run arbitrary commands without credentials. CISA added it to the KEV catalog on 13 October 2026. The FAQ lists affected branches by ISA hardware (25.1.1.1, 25.1.2.2, 22.8.X), fixed versions (25.1.1.2, 25.1.3.0/25.1.3.1, 22.8R2.5), no workaround and no reliable IOCs.
watchtowr.comadvisoryAdded 30 Oct 2026, published 13 Oct 2026🛡️ Security Ivanti Connect Secure Authentication Bypass by Spoofing (CVE-2026-104935)
CVE-2026-104935 is an authentication bypass by spoofing in Ivanti Connect Secure (CVSS 3.1 score 8.6) that lets a remote attacker run commands without logging in. CISA added it to KEV on 13 October 2026. The 22.8.X bridge release and 25.1.2.2 and earlier are affected, with fixes in 22.8R2.5, 25.1.1.2, 25.1.3.0 and 25.1.3.1. Ivanti says no reliable indicators of compromise exist yet.
watchtowr.comadvisoryAdded 30 Oct 2026, published 13 Oct 2026🛡️ Security- AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
Guided tour of Omar Santos's eight-part AI-agents-for-cybersecurity repository. It moves from LLM building blocks (LangChain, RAG) to security agents built with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan). It also covers a hardening guide for six agentic frameworks, token-cost control, and a spec for a supervisor-led, human-gated assessment harness. Design lessons include least-privilege subagents, single-use approvals and kill switches.
 becomingahacker.orgarticleAdded 13 Oct 2026🧠 AI
- santosomar/AI-agents-for-cybersecurity
Companion repository for Omar Santos's Pearson and O'Reilly trainings and books. It has eight parts of runnable Python labs: chat models, embeddings, prompt templates, LCEL prompt chaining, Chroma-based RAG, ReAct/LangGraph/CrewAI/DeepAgents agents, and FastMCP servers (nmap, CISA KEV, Shodan). It also includes guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz), a tokenomics module on agent cost (context compounding, prompt caching, model routing, token budget guards, batch API, cost per accepted outcome), and a vendor-neutral design spec for a human-gated multi-agent assessment harness. It is a current, practical curriculum for building and operating agents. Some examples act on real systems and should only be run in an authorized lab.
 github.comrepoAdded 13 Oct 2026🧠 AI
- santosomar/AI-agents-for-cybersecurity
Omar Santos's companion repo for his Pearson/O'Reilly trainings and books, organised in eight parts. They cover LangChain prompts, chains and RAG (Chroma), and agents (LangGraph, CrewAI, DeepAgents). They also cover FastMCP security servers (nmap, CISA KEV, Shodan) and attack-surface-management and SOC agent examples. Later parts have security guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz) with hardening notes and 2026 CVE mapping, agent cost/tokenomics scripts including denial-of-wallet budget guards, and a vendor-neutral spec for a human-gated multi-agent security-assessment harness (scope manifest, approval gates, kill switch). Useful as a hands-on path into AI-agent security tooling, with warnings that some examples act on real systems.
github.comrepoAdded 13 Oct 2026🛡️ Security - AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
Omar Santos walks through his eight-part AI-agents-for-cybersecurity repository: LLM building blocks (LangChain, RAG), then security agents with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan), a hardening guide for six agentic frameworks, token-cost control for agents, and a spec for a supervisor-led, human-gated security-assessment harness. It covers concrete design lessons such as least-privilege subagents, staged response actions, single-use approvals bound to exact actions, kill switches, and mapping controls to the OWASP Top 10 for Agentic Applications. Also notes Project CodeGuard rules shipped for AI coding assistants.
becomingahacker.orgarticleAdded 13 Oct 2026🛡️ Security - AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
Omar Santos walks through his AI-agents-for-cybersecurity GitHub repo, which has eight parts. Parts 1–4 cover LLM basics (LangChain, prompting, LCEL, RAG). Parts 5–8 cover building security agents with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan), and a hardening baseline for six ready-made agentic frameworks. They also cover token-cost control (caching, routing, budget guards, cost per accepted outcome) and a supervisor-led, human-gated security-assessment harness spec with single-use approvals, a kill switch and an append-only audit log. The post also covers Project CodeGuard rules for AI coding assistants. It is a practical learning path and a reference for governing and securing agents.
 linkedin.comarticleAdded 13 Oct 2026🛡️ Security
 The OWASP Top 10 Gets Modernized | Endor Labs
Commentary on the 2025 OWASP Top 10 update presented at OWASP Global AppSec in Washington, D.C. Broken Access Control stays #1, Security Misconfiguration and the new Software Supply Chain Failures category (replacing Vulnerable and Outdated Components) rise to #2 and #3, and Cryptographic Failures, Injection and Insecure Design drop. The author adds context on agentic AI and MCP identity and authorization, AI-assisted SAST, non-human identities, CISA Secure-by-Default, OWASP SPVS, and slopsquatting and AI coding assistant risks.
endorlabs.comarticlePublished and added 12 Oct 2026🛡️ Security- ThreatWire (@ThreatWire_) on X
Post announcing a public PoC for CVE-2026-13043, a critical flaw (CVSS 4.0 9.3, scored by WatchGuard) in PSKMAD, the kernel memory access driver of WatchGuard Endpoint Security on Windows. The access-control handshake can be bypassed (CWE-306/CWE-798), letting a local authenticated attacker send privileged commands and read kernel and other processes' memory. Fixed in 8.00.26.0012; the PoC author and LOLDrivers frame the signed driver as BYOVD material, which WatchGuard does not say. The post notes it is not in CISA KEV, has no reported in-the-wild exploitation, and that ThreatWire has not run the PoC.
x.comthreadAdded 11 Oct 2026, published 10 Oct 2026🛡️ Security - CISA AA26-281A: Chinese Government-linked Actors Combine Automated and Hands-on Hacking Tools to Steal Data
Joint FBI/CISA/NSA and allied-agency advisory on China-linked actors enabled by Integrity Technology Group (overlapping with Flax Typhoon, Ethereal Panda, Red Juliett). It details their TTPs: open-source scanners and the MicroScan exploit-script app, an XSS credential-harvesting payload dropping live700_v1.exe, EBurst password spraying against Exchange/O365, SoftEther VPN persistence, DCSync via DC.exe, and email theft via the Curlc4.txt PHP bot and the office-cli utility. It also provides IOCs, MITRE ATT&CK mappings, CVEs, incident response steps, and mitigations.
cisa.govadvisoryAdded 9 Oct 2026🛡️ Security  In Other News: AI Used in Korean Bank Breaches, Poem-Guided Botnet, Empire Admin Gets 40 Years
SecurityWeek's weekly news digest covering PoeLLM malware that resolves its C&C IP from keywords hidden in a GitHub-hosted poem, the GhostAction campaign spreading malicious GitHub Actions workflows to steal secrets from 772 more repos, South Korean authorities probing suspected AI-assisted bank breaches where CrowdStrike found Claude Code and Claude memory artifacts on attacker infrastructure, a high-severity Nvidia DCGM Exporter flaw (CVE-2026-47483) exposing GPU telemetry from over 12,000 hosts, and a Shai-Hulud-style credential-stealing worm shipped in Tensorlake's npm SDK. Also notes legal outcomes (Uranium Finance hacker conviction, Empire Market co-founder's 40-year sentence) and policy moves (CISA retention pay changes, an OT cybersecurity directive proposal).
securityweek.comarticlePublished and added 9 Oct 2026🛡️ Security- Dark Web Intelligence (@DailyDarkWeb) on X
A Twitter/X post digests joint advisory AA26-281A from FBI, CISA, NSA and allied agencies (UK, Australia, Canada, Japan, New Zealand, Spain) on China-based Integrity Technology Group enabling threat actors, tracked elsewhere as Flax Typhoon, Ethereal Panda and Red Juliett, to target US critical infrastructure, government, healthcare, education and law enforcement networks worldwide. The actors chain open-source scanners, large botnets, XSS, password spraying against Microsoft Exchange, VPN persistence and credential-harvesting scripts. CISA added five exploited CVEs (ISC BIND, Apache Struts, ProFTPD, ONLYOFFICE Docs, Strapi) to its KEV catalog with an Oct 11 federal remediation deadline, and STIX IOCs accompany the advisory.
x.comthreadPublished and added 8 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
A detailed "CVE of the Day" thread analyzing CVE-2026-76471, a critical (CVSS 9.8) Cisco advisory covering insufficient NX-API input validation (CWE-122 heap-based buffer overflow) on Nexus 3000/9000 standalone NX-OS and a lower-severity credentialed variant on UCS 6300 Fabric Interconnects via UCS Manager XML API. It compiles Cisco's fixed-software versions per platform, notes the temporary Live Protect shield lp00074, and walks through a six-step SOC evidence-preservation and correlation playbook (scoping affected devices, preserving logs/crash artifacts, reviewing API/shield telemetry, correlating device outcomes, remediating, and verifying post-patch state) while flagging that CISA KEV and FIRST EPSS had no data on the CVE at research time.
x.comwriteupPublished and added 8 Oct 2026🛡️ Security  Top MCP security resources — October 2026
Adversa AI's October 2026 MCP security roundup, aggregating and synthesizing 15 resources: authentication-bypass vulnerabilities in LiteLLM's MCP endpoint (CVE-2026-59822, now CISA KEV), Grafana's MCP server session spoofing/SSRF (CVE-2026-19516), an MCP Python SDK OAuth-fallback flaw exploited by a malicious server returning a 404, and an Obot gateway route-matching bypass reopening GHSA-vw82. It also covers detection failures (two malicious MCP servers passing five scanners including Cisco mcp-scanner and Snyk agent-scan, 12% of 82,000 public MCP configs hardcoding secrets), a malicious npm wallet-signing package (gadgethumans-mcp), the A2M agent-hijacking attack technique, and CoSAI's MCP Security v2.0 governance model.
 adversa.aiarticlePublished and added 8 Oct 2026🛡️ Security
 Configuring your AI vulnerability harness, Part 2: The steering file
AWS Security Blog's second post in a series on building an "AI vulnerability harness" explains the configuration (steering file) that stops an AI model from hallucinating vulnerabilities and inflating severity during security code review. It details five configuration sections — structural verification of findings, an evidence-based confidence formula (weighting confirmed taint flow at 0.30), infrastructure-aware severity multipliers for controls like AWS WAF and IAM, CISA KEV/EPSS threat-intel boosting, and a four-tier priority classification — and reports validation numbers (e.g., unsteered models fabricated code paths in ~30% of findings; steered confidence of HIGH without structural confirmation was only 34% exploitable vs 89% with confirmed taint). The steering file is shipped as a Kiro steering file, a Kiro skill, and a CLAUDE.md for Claude Code, with full source in a linked GitHub repo.
aws.amazon.comarticlePublished and added 7 Oct 2026🛡️ Security- Configuring your AI vulnerability harness, Part 2: The steering file
Part 2 of an AWS Security Blog series detailing the design of a "steering file" — a persistent instruction set (deployable as a Kiro steering file, Kiro skill, or Claude Code CLAUDE.md) that constrains an LLM performing vulnerability triage. It walks through five configuration sections: requiring structural/dataflow verification before reporting findings, replacing self-reported confidence with a weighted formula based on binary structural signals (e.g., 0.30 weight for confirmed taint flow), mapping infrastructure controls (AWS WAF, IAM) to severity multipliers with a 0.15 floor, incorporating CISA KEV and EPSS threat-intelligence boosts capped at +0.50, and a four-tier priority classification that suppresses low-confidence P3 findings. Validation against a 10-vulnerability test app showed the steered model eliminated fabricated findings and correctly downgraded mitigated vulnerabilities while preserving full severity for a command injection reachable only via authenticated access.
aws.amazon.comwriteupAdded 8 Oct 2026, published 7 Oct 2026🧠 AI  Atlassian Jira, Confluence (and more) Arbitrary File Read Vulnerability (CVE-2026-21589)
CVE-2026-21589 is an unauthenticated arbitrary file read (path traversal) in eight Atlassian Data Center and Server products: Bitbucket, Confluence, Jira, Jira Service Management, Bamboo, Crowd, Crucible and Fisheye. Atlassian fixed it on 5 October 2026, and CISA added it to the KEV catalog on 15 October 2026. The page lists patching, WAF regex, Tomcat RewriteValve and urlrewrite.xml mitigations, and a log check for ".." sequences after up to two rounds of URL decoding.
watchtowr.comadvisoryAdded 30 Oct 2026, published 6 Oct 2026🛡️ Security- Dark Web Intelligence (@DailyDarkWeb) on X
Atlassian disclosed CVE-2026-21589, a critical (CVSS 9.3) unauthenticated path traversal flaw allowing remote attackers to read specific files within the web application root across its self-managed Data Center/Server products — Jira Software, Jira Service Management, Confluence, Bitbucket, Bamboo, Crowd, Crucible, and Fisheye. Fixed versions are listed for each product (e.g. Jira 9.12.40/10.3.26/11.3.12, Confluence 9.2.26/10.2.19), and Atlassian Cloud is already patched; WAF/URL-rewrite mitigations are available for those who can't upgrade immediately. The post's analyst note clarifies exploitation requires knowing the exact target file path (no directory listing), and as of Oct 5, 2026 it is not yet in CISA KEV with no public exploit reported.
x.comadvisoryAdded 7 Oct 2026, published 6 Oct 2026🛡️ Security  Citrix NetScaler Zero-Day Exploited in the Wild Crashes SAML Authentication Services
Analysis of CVE-2026-88779 (CVSS v4.0 8.7), an unauthenticated memory-overflow flaw in the nsaaad SAML authentication handler on Citrix NetScaler ADC/Gateway that lets attackers crash the SAML service and lock out VPN/SSO access indefinitely through repeated triggering. Affects NetScaler 14.1 before 14.1-73.41 and 13.1 before 13.1-64.28 (plus FIPS/NDcPP builds); watchTowr Labs reproduced it via honeypot activity, Citrix confirmed targeted in-the-wild exploitation from IP 213.209.159.55, and CISA added it to KEV on 2026-10-04 with an Oct 7 federal remediation deadline. Some researchers suspect the overflow could extend to RCE beyond the documented DoS, though Citrix hasn't confirmed this.
orca.securityadvisoryPublished and added 5 Oct 2026🛡️ Security- CISA KEV: Fortinet FortiMail CVE-2026-104286 path traversal, actively exploited, no patch yet
CISA added CVE-2026-104286, a path traversal vulnerability in Fortinet FortiMail, to its Known Exploited Vulnerabilities Catalog on evidence of active exploitation. The alert restates the obligations of BOD 26-04 for Federal Civilian Executive Branch agencies: prioritise KEV CVEs on publicly exposed assets that give total control, and check for compromise before patching. It also describes the KEV nomination criteria: a CVE ID, evidence of exploitation and clear mitigation guidance. The page gives no technical detail, patch status or IOCs.
cisa.govadvisoryAdded 4 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
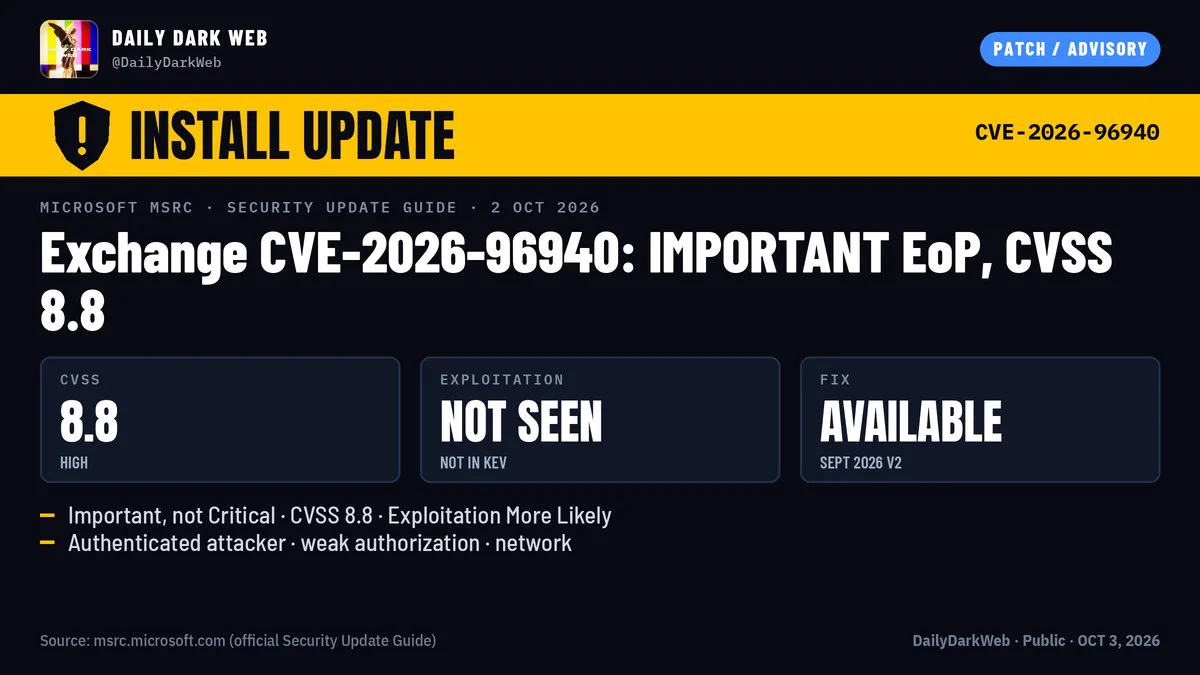
Summary of Microsoft's September 2026 V2 / October 2026 early security updates adding CVE-2026-96940, an Important elevation-of-privilege flaw (CVSS 8.8) in on-prem Exchange Server caused by weak authorization that lets an authenticated attacker escalate privileges over the network. Covers affected builds and KBs (Exchange SE RTM KB5129955, 2019 CU15/CU14 KB5129956/5129957, 2016 CU23 KB5129958) and notes Exchange Online is unaffected, the flaw was found internally by Microsoft with no known exploitation and is not in CISA KEV.
x.comthreadAdded 4 Oct 2026, published 3 Oct 2026🛡️ Security  Critical FortiMail Zero-Day Flaw (CVE-2026-104286)
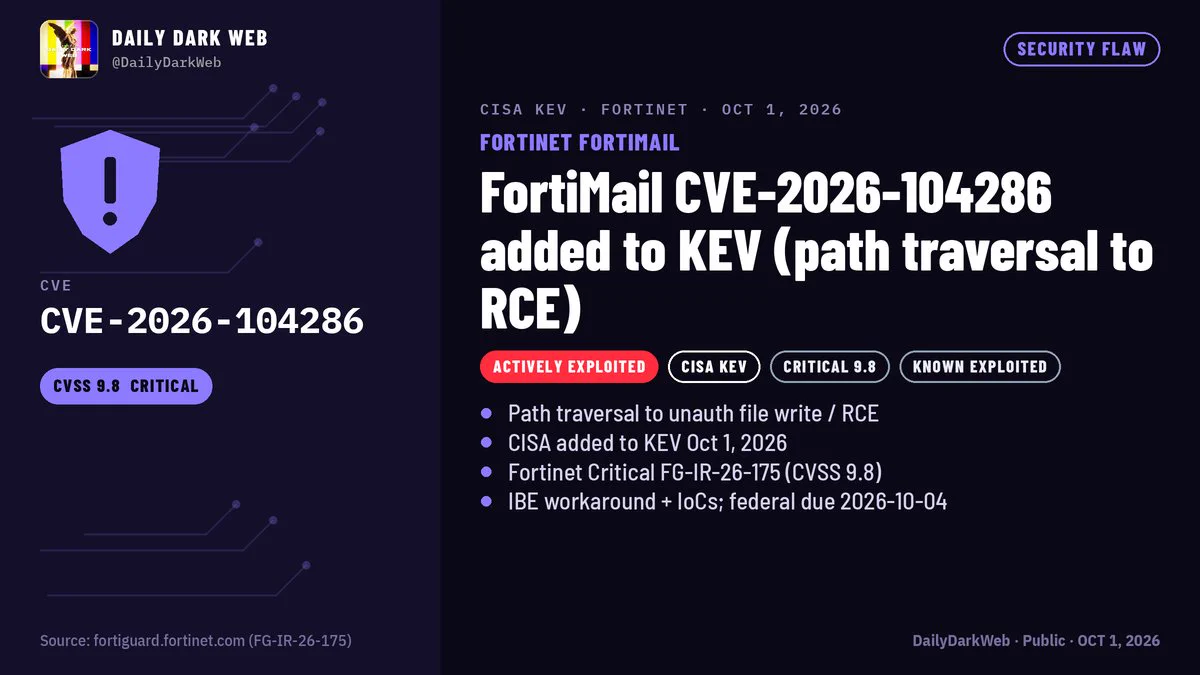
CISA added CVE-2026-104286 (CVSS 9.8), a path traversal and NULL-byte handling flaw in Fortinet FortiMail, to its Known Exploited Vulnerabilities catalog after confirming active in-the-wild exploitation. The bug lets unauthenticated attackers write arbitrary files via crafted HTTP/HTTPS requests, affecting FortiMail 7.2 through 8.0.1; Fortinet published workarounds (disabling IBE, restricting management-interface access) ahead of patches and shared attacker IPs and modified/added files as IOCs. The article also lists several other actively exploited vendor flaws disclosed the same week (Check Point, Arista VeloCloud, F5 BIG-IP APM, Cisco Catalyst SD-WAN Manager, Citrix NetScaler).
 thehackernews.comadvisoryAdded 3 Oct 2026🛡️ Security
- The First 24 Hours: What Happens When Ransomware Lands
An hour-by-hour ransomware incident response playbook written by UnderDefense CEO Nazar Tymoshyk and published on Huntress's blog, covering confirmation, containment, exfiltration detection, backup/recovery pitfalls, and root-cause investigation in the first 24 hours of an attack. It draws on Mandiant's M-Trends 2026 report (14-day median dwell time, 22-second access-broker-to-ransomware handoff) and CISA's November 2025 Akira advisory (VPN without MFA as primary access vector, exfiltration via FileZilla, WinRAR, WinSCP, RClone, Mega and Ngrok, credential dumping with Mimikatz and LaZagne, PowerShell-based shadow copy deletion) alongside real UnderDefense engagement anecdotes.
 huntress.comwriteupAdded 3 Oct 2026, published 2 Oct 2026🛡️ Security
 SMTP is the key: BPFDoor and AVERAT hitting the network edge
Rapid7 details a new BPFDoor campaign targeting telecom and network-edge appliances (ShareTech, SpamSniper mail gateways) and a six-sample Linux RAT family dubbed AVERAT found on compromised Taiwanese CPE (Synology NAS, a NetKlass device, a Dahua DVR). The writeup reconstructs the Rapid7 BPFDoor controller's HTTP-tunneled trigger mechanism, a fileless ShareTech dropper that stages binaries as ntpdate/udevds and deletes them while processes keep running, a BPF Rekoobe variant that hides inside SMTP port-25 traffic, and AVERAT's RC4-derived config/C2 scheme — tying the infrastructure to the broader China-nexus ORB (Operational Relay Box) device pattern described in CISA/NCSC-UK advisory AA26-113A. It closes with detection guidance for unlinked/deleted process execution, dropper staging artifacts, and port-25 C2 callbacks, plus full IOC and ATT&CK tables.
rapid7.comwriteupAdded 7 Oct 2026, published 2 Oct 2026🛡️ Security Five Kubernetes Security Gaps Attackers Chain Together
7ASecurity breaks down five Kubernetes misconfiguration categories their pentesters repeatedly chain into working attack paths: over-permissive RBAC defaults, exposed API server/dashboard/kubelet, missing network policies, unsafe pod defaults (root/privileged containers, host path mounts), and weak admission control. It uses a concrete audit example from CNCF's KEDA project, where the Helm chart's scaledRefKinds setting defaulted to wildcard get access across API groups and resource types, silently undermining KEDA's own Secret-access restriction, plus references to Linkerd mesh audits and the NSA/CISA Kubernetes Hardening Guide.
 7asecurity.comarticleAdded 7 Oct 2026, published 2 Oct 2026🛡️ Security
- Dark Web Intelligence (@DailyDarkWeb) on X
CISA added CVE-2026-104286, a critical (CVSS 9.8) path traversal and NULL-byte neutralization flaw in Fortinet FortiMail, to its Known Exploited Vulnerabilities catalog on October 1, 2026, citing active in-the-wild exploitation. The bug allows unauthenticated arbitrary file write via crafted HTTP/HTTPS requests on FortiMail 7.2.0–7.2.9, 7.4.0–7.4.8, 7.6.0–7.6.6, and 8.0.0–8.0.1, with fixes coming in 8.0.2/7.6.7/7.4.9+ and an interim workaround of disabling IBE and restricting management-interface internet access. Federal agencies face an October 4, 2026 BOD 26-04 remediation deadline, and Fortinet's advisory (FG-IR-26-175) includes IoCs for hunting.
x.comthreadAdded 2 Oct 2026, published 1 Oct 2026🛡️ Security - Critical Cisco Catalyst SD-WAN Manager API authentication bypass exploited in the wild (CVE-2026-76504)
Rapid7 analysis of CVE-2026-76504, a critical (CVSSv3.1 9.8) unauthenticated API authentication bypass in Cisco Catalyst SD-WAN Manager caused by improper URL-encoding handling (CWE-177), allowing attackers to gain admin-level API access via crafted requests to the j_security_check endpoint. The flaw is being actively exploited in the wild, was added to CISA's KEV list on October 1, 2026 with a remediation deadline of October 3, and follows two earlier 2026 Catalyst SD-WAN peering authentication bypasses (CVE-2026-20127 and Rapid7-discovered CVE-2026-20182). The post gives fixed-release guidance, no-workaround caveats, and log-based IOCs (encoded-character requests like %6a_security_check, viptela-reserved- usernames) for detecting compromise.
rapid7.comadvisoryAdded 7 Oct 2026, published 30 Sep 2026🛡️ Security  lee1981 (@lee1981b) on X
A detailed breakdown of CVE-2026-102710 (CVSS v4.0 9.3), a privilege-escalation flaw in Eclipse ThreadX RTOS builds with event tracing enabled: a module-supplied trace callback pointer is retained by the kernel and invoked with kernel privilege when the trace buffer wraps, letting an attacker who already controls a memory-protected user-mode module fault the kernel or execute code in kernel context. The thread walks through the vulnerable code path (registration, storage, invocation across the protection boundary), CWE-269/CWE-822 classification, affected versions (through v6.5.1.202602a_rel), and provides a defender hunting guide plus emergency remediation steps, noting no fixed upstream release or CISA KEV/EPSS entry exists yet.
x.comthreadPublished and added 30 Sep 2026🛡️ Security Critical Citrix NetScaler Zero-Days Under Active Exploitation
Analysis of two CVSS 9.5 Citrix NetScaler ADC/Gateway zero-days, CVE-2026-88771 (unauthenticated RCE through improper input validation in the management interface, affecting default deployments) and CVE-2026-88772 (memory overflow in DTLS, enabled by default on VPN virtual servers). It lists six more high-severity flaws patched in advisory CTX697096, the affected and fixed versions, and the CISA KEV listing with a federal deadline of 2026-09-30. It advises checking for compromise before patching, since patching can destroy forensic evidence, and gives response steps: isolate, revoke credentials, rebuild firmware, rotate keys and certificates.
orca.securityadvisoryPublished and added 29 Sep 2026🛡️ Security- Critical Zero-Day Vulnerabilities Exploited in Citrix NetScaler ADC, Gateway
CISA alert amplifying Citrix's disclosure of ten NetScaler ADC and Gateway vulnerabilities (CVE-2026-88771 to CVE-2026-88779 and CVE-2026-107406). CVE-2026-88771 and CVE-2026-88772 are critical zero-days enabling independent remote code execution and are exploited globally; CVE-2026-88779 is a SAML SP/IdP denial-of-service that can force a reboot to trigger code injected via CVE-2026-88771. It advises checking for compromise before patching, preserving forensic evidence, forwarding logs to a SIEM, restoring a pre-compromise backup and rotating all secrets, and links a CISA SIGMA detection rule.
cisa.govadvisoryAdded 28 Sep 2026🛡️ Security - Zero-Day Exploitation of Citrix NetScaler ADC and Gateway: CVE-2026-88771 and CVE-2026-88772
Rapid7 details active zero-day exploitation of two critical Citrix NetScaler ADC/Gateway RCE vulnerabilities (CVE-2026-88771, CVE-2026-88772, both CVSSv4 9.5), both added to CISA KEV on disclosure day, plus a later SAML denial-of-service zero-day (CVE-2026-88779). The post includes Rapid7 MDR's observed exploitation of CVE-2026-88771 in the wild — a command-injection payload that exfiltrates /flash/nsconfig (containing ns.conf admin credentials, SSL private keys, SSH host keys) via the publicly-served /vpn/ path, and a webshell (SHA256 hash provided) found on a compromised appliance — along with vendor patch versions and detection guidance.
rapid7.comadvisoryAdded 7 Oct 2026, published 28 Sep 2026🛡️ Security  watchTowr: CVE-2026-88771 Citrix NetScaler ADC/Gateway unauthenticated RCE
watchTowr details CVE-2026-88771 (unauthenticated command execution via improper input validation, affecting every NetScaler ADC/Gateway deployment by default) and CVE-2026-88772 (DTLS memory overflow leading to RCE/DoS, exploitable since DTLS is on by default for VPN virtual servers). Both are confirmed exploited in the wild as zero-days, were pre-notified by NCSC-NL, and CVE-2026-88771 was added to the CISA KEV catalog on September 27, 2026; Citrix's bulletin CTX697096 also fixes six related issues (CVE-2026-88773 through CVE-2026-88778). The writeup gives prioritization guidance, IOC-checking steps, and warns that patching may destroy forensic evidence if done before evidence capture.
watchtowr.comadvisoryAdded 5 Oct 2026, published 27 Sep 2026🛡️ Security







Showing 90 of 140
Show more