 CISA says max severity GitLab flaw now exploited in the wild
CVE-2026-97229 is a maximum-severity GitLab flaw in the CI/CD Regular Expression Compiler, caused by an integer overflow, that lets unauthenticated attackers run code via a crafted regular expression. CISA added it to the KEV Catalog and ordered federal agencies to patch under BOD 26-04. GitLab fixed it in CE/EE 19.4.2, 19.3.5 and 19.2.8, and Shadowserver tracks about 2,800 exposed CE instances.
 bleepingcomputer.comarticlePublished and added 30 Oct 2026🛡️ Security
 Drupal warns of critical Commerce Core flaw exploited in attacks
Drupal Commerce Core has a critical missing-authorization flaw, CVE-2026-118539, that unauthenticated attackers exploit in the wild. It affects versions 0.0.0 to 2.41 and 3.0.0 to 3.3.13. Drupal urges upgrading to 3.3.13 (or 8.x-2.41 on the older branch) and auditing orders for inconsistencies. The article also recalls CVE-2026-9082, exploited in May and added to CISA KEV, and two RCE patches (CVE-2026-108097, CVE-2026-108099).
bleepingcomputer.comarticlePublished and added 30 Oct 2026🛡️ Security Max-Severity GitLab Vulnerability Exploited Against Alpine Linux
CVE-2026-97229 is a CVSS 10 code execution flaw in Onigmo, Ruby's regular expression engine, reachable through crafted CI/CD configuration in GitLab. Attackers used it against Alpine Linux's GitLab on 20 and 21 October 2026 and failed; Alpine rebuilt the instance and found no tampering with aports or packages. Self-managed installs with their own Ruby need Ruby 3.3.13, 3.4.12 or 4.0.9, not just GitLab 19.3.6. CISA added it to KEV.
 securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security
 A quiet week in infosec <.<
Cisco Talos Threat Source newsletter for the week of the PHP and Node.js vulnerability news cycle. It summarises NIK C2, a Go-based Windows implant that dumps credentials, streams keystrokes, deploys screen-locking ransomware and uses a victim's hijacked OpenAI API keys to analyse stolen data. It also lists weekly headlines (CISA KEV PHP bugs, Brotli flaw, Gheist GitHub token theft), Talos links and top malware hashes.
 blog.talosintelligence.comarticlePublished and added 29 Oct 2026🛡️ Security
 CISA warns of Fragnesia Linux flaw chained in PHP2Shell attacks
Fragnesia (CVE-2026-46300) is a Linux kernel XFRM ESP-in-TCP logic bug in the Dirty Frag class that gives local attackers root, with a public PoC. CISA added it to the KEV catalog and ordered federal patching under BOD 26-04. Attackers chain it with PHP2Shell (CVE-2026-109618, CVE-2026-109619) to implant PHP webshells. Dream Security tied the chain to 25 rooted servers in the US, Japan, Taiwan and South Korea.
bleepingcomputer.comarticleAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security- Chinese Hackers Quietly Used Low-Severity ESXi Logging Flaw as Zero-Day
CVE-2026-41709 is a low-severity insufficient-logging flaw in VMware ESXi that lets a logged-in administrator perform operations without audit entries. CISA added it to the KEV catalog, and CrowdStrike reported that China-nexus actor Warp Panda used it as a zero-day against US organizations, including law firms, to cut audit visibility. The article also covers exploitation of vCenter bugs CVE-2026-59309 and CVE-2026-59310 and lists the fixed ESXi builds.
securityweek.comarticlePublished and added 29 Oct 2026🛡️ Security  CISA Warns of Node2Shell Exploitation as Honeypots Log Attack Attempts
CVE-2026-111497 (Node2Shell, also HTTP2Shell and Broccoli2Shell) is an out-of-bounds write in the Brotli decoder, affecting versions 1.0.3 through 1.2.0. CISA added it to the KEV catalog on 27 October 2026 with a federal deadline of 10 November. Previdian and ELLIO logged exploitation attempts; ELLIO found the observed exploit broken but achieved code execution itself, and Broadcom's VMware SDDC Manager patches are pending.
securityweek.comarticlePublished and added 28 Oct 2026🛡️ Security This is Fine: What NetScaler Zero-Days Tell Us About the New Normal
This SecurityWeek commentary covers the September 2026 Citrix NetScaler ADC and Gateway zero-days, exploited from mid-month and patched on 27 September as unauthenticated RCE flaws CVE-2026-88771 through CVE-2026-88778. The author argues the fast response shows stronger defence. Cited evidence: Citrix disclosure time fell from about 40 days to 17 in 2026 after it set up a NetScaler CNA, and CISA made a rare Sunday KEV addition.
securityweek.comarticlePublished and added 27 Oct 2026🛡️ Security Maritime Coalition Launches Free Vulnerability Database for Ship and Port Systems
Blue Initiative is a free public vulnerability database for maritime IT and OT, built by Cydome, ClassNK, Bureau Veritas, MTS-ISAC and Rakuten Maritime. It holds nearly 30,000 entries, over 2,000 rated critical by CVSS and more than 580 known exploited. Only 37 affect ship and port products. Most entries are pulled from CISA ICS advisories and the KEV catalog and mapped to maritime systems.
securityweek.comarticlePublished and added 27 Oct 2026🛡️ Security PHP2Shell Exploitation Moves From Probes to Working Shells
PHP2Shell exploitation (CVE-2026-109618, CVE-2026-109619) reached working shells on 24 October 2026, when Perplexity researcher Adel Karimi's honeypots (PHP 8.4.26, Apache mod_php, single worker) logged 35 shells across three servers. Attackers used a four-stage HTTP chain: memory exhaustion, memory leak, then shell command execution, matching a public PoC. No second-stage payload was seen, and CISA had not added the flaws to KEV as of 26 October.
securityweek.comarticlePublished and added 26 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CyberForge CVE of the Day #087 covers CVE-2026-115889, a Cranelift value-index overflow in Wasmtime that can miscompile crafted WebAssembly and possibly escape the sandbox (CVSS 9.9, CWE-197 and CWE-843). Affected: below 36.0.19, and 37.0.0 up to but excluding 43.0.0; fixes are 36.0.19 and 43.0.0. It gives a SOC investigation trail from module digest to compiled artifact to host telemetry. EPSS is 0.454%, with no KEV entry.
 x.comarticleAdded 28 Oct 2026, published 26 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CyberForge Weekly CVE Rundown #007 covers six CVEs from 19 to 24 October 2026: SiteGuard command injection (CVE-2026-106931), DB-GPT (CVE-2026-77932), Siemens Software Center DLL side-loading (CVE-2026-110936), Cisco Expressway (CVE-2026-76466), Node.js Brotli (CVE-2026-111497) and Arista VeloCloud (CVE-2026-114625). Each entry gives defender actions, fixed versions, exploitation status and primary-source links. Updated 25 October 2026 with CISA KEV and EPSS findings.
x.comarticleAdded 27 Oct 2026, published 25 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CVE-2026-110936 is an uncontrolled DLL search path flaw (CWE-427) in Siemens Software Center below V4.0.9.8, listed in CISA KEV on 20 October 2026. The post covers CVSS v4.0 8.4 and v3.1 6.7, Siemens' Romulus ClickFix campaign indicators (IPs, domain, hashes, file leads) and a six-step SOC trail using Sysmon, EDR and network records. It separates delivery from DLL load and from compromise.
x.comarticleAdded 24 Oct 2026, published 21 Oct 2026🛡️ Security  There's only so much code: the rise in vulnerability numbers
Cisco Talos analysis of why Microsoft Patch Tuesday advisories rose from about 100 a month before June 2026 to 975 in September and 1,415 in October, as frontier models such as Mythos mine old code. CVEs grew 105% year over year while CISA KEV additions grew 37%, and only three September advisories were exploited in the wild. It covers pressure on 90-day coordinated disclosure and open-source maintainers, the format string bug-class precedent, and defender advice.
blog.talosintelligence.comarticlePublished and added 20 Oct 2026🛡️ Security Exploited Fortinet Bug Linked to Stealthy FortiGate Implant in Telecom Hack
UNC5820 (tracked by Palo Alto Networks as CL-STA-0954) breached a telecom in September 2024 using FortiManager flaw CVE-2024-47575 (FortiJump) and path traversal CVE-2025-61624, then deployed PeerStitch, a memory-resident ARM64 FortiGate implant. PeerStitch patches FortiOS log and IKE/IPsec daemons to build a covert bridge without listening ports. The actor also impersonated FortiManager over FGFM, using CVE-2024-26008. CISA added CVE-2025-61624 to KEV.
securityweek.comarticlePublished and added 19 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CyberForge Weekly CVE Rundown #006 covers six CVEs from 12-17 October 2026: BotSharp default signing key, GitLab CI/CD regex compiler overflow (CVSS v3.1 10.0), Ivanti Connect Secure auth bypass, Cisco Secure Email Gateway, BeyondTrust Remote Support and the Linux kernel PwnEscape guest-to-host bug. It gives fixed versions, KEV and EPSS status as of 18 October, and separates patch verification from compromise investigation.
x.comarticleAdded 20 Oct 2026, published 18 Oct 2026🛡️ Security  The Q3 Vulnerability Pulse: Discovery ≠ Exploitation
Talos Threat Source newsletter arguing that record CVE volume (over 70k by end of Q3, six-digit CVE IDs) is not the same as exploitation. KEV grew only 37% YoY against 105% for CVEs, about a third of KEV entries are CVEs from 2025 or earlier (a patch gap), and 29% of 2026 KEV CVEs were added on their publication date. It also notes the new KEV "forensicTriage" column (BOD 26-04), summarizes the Talos/Insikt report on UAT-6275 espionage against CIS governments with GitHub-hosted payloads and a WinRAR exploit, and lists weekly headlines.
blog.talosintelligence.comarticlePublished and added 15 Oct 2026🛡️ Security Palo Alto Networks Patches PAN-OS Zero-Day Exploited for Remote Code Execution
Palo Alto Networks patched CVE-2026-0322, a high-severity zero-day in the PAN-OS management interface that lets an authenticated attacker with network access run arbitrary code as root. It affects PA-Series, VM-Series and Panorama with no special configuration needed, and "very limited" exploitation has been seen. The vendor published a few IP-based IoCs, CISA added the flaw to KEV with an October 17 deadline, and a dozen other medium/low advisories were released the same day.
securityweek.comarticlePublished and added 15 Oct 2026🛡️ Security Cisco Warns of Exploited Secure Email Gateway Vulnerability
Cisco warned that CVE-2026-76519 (CVSS 9.8), an unauthenticated arbitrary file write in the Advanced Malware Protection feature of Secure Email Gateway, is exploited in the wild. Crafted email attachments can lead to root command execution when file reputation is enabled and Content Scanner Tools is older than 25.3.0.5525. Fixes shipped September 14 in AsyncOS 15.5.5-014 and 16.5.0-780. Cisco published IoCs, advises rebuilding virtual appliances and rotating credentials, and CISA added the flaw to KEV. It is the second exploited SEG bug since mid-September, after CVE-2026-76461.
securityweek.comarticlePublished and added 15 Oct 2026🛡️ Security Microsoft Patches Record 1,413 Vulnerabilities, Including Exploited Windows Zero-Day
SecurityWeek reports Microsoft's October 2026 Patch Tuesday fixed a record 1,413 CVEs (1,102 in Windows, 134 Office, 36 SharePoint), more than all of 2025, with the surge attributed largely to AI-driven discovery. The exploited zero-day CVE-2026-96951 is a Windows shell Mark of the Web security feature bypass (CVSS 8.8), added to CISA KEV with an October 16 deadline. Two flaws were publicly disclosed: CVE-2026-108398 (WDAC bypass) and CVE-2026-92707 (MessagePack-CSharp DoS), and Microsoft introduced 'risk cohorts' for patch prioritization.
securityweek.comarticlePublished and added 14 Oct 2026🛡️ Security- AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
Guided tour of Omar Santos's eight-part AI-agents-for-cybersecurity repository. It moves from LLM building blocks (LangChain, RAG) to security agents built with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan). It also covers a hardening guide for six agentic frameworks, token-cost control, and a spec for a supervisor-led, human-gated assessment harness. Design lessons include least-privilege subagents, single-use approvals and kill switches.
 becomingahacker.orgarticleAdded 13 Oct 2026🧠 AI
- AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
Omar Santos walks through his eight-part AI-agents-for-cybersecurity repository: LLM building blocks (LangChain, RAG), then security agents with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan), a hardening guide for six agentic frameworks, token-cost control for agents, and a spec for a supervisor-led, human-gated security-assessment harness. It covers concrete design lessons such as least-privilege subagents, staged response actions, single-use approvals bound to exact actions, kill switches, and mapping controls to the OWASP Top 10 for Agentic Applications. Also notes Project CodeGuard rules shipped for AI coding assistants.
becomingahacker.orgarticleAdded 13 Oct 2026🛡️ Security - AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
Omar Santos walks through his AI-agents-for-cybersecurity GitHub repo, which has eight parts. Parts 1–4 cover LLM basics (LangChain, prompting, LCEL, RAG). Parts 5–8 cover building security agents with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan), and a hardening baseline for six ready-made agentic frameworks. They also cover token-cost control (caching, routing, budget guards, cost per accepted outcome) and a supervisor-led, human-gated security-assessment harness spec with single-use approvals, a kill switch and an append-only audit log. The post also covers Project CodeGuard rules for AI coding assistants. It is a practical learning path and a reference for governing and securing agents.
 linkedin.comarticleAdded 13 Oct 2026🛡️ Security
 Critical SonicWall Vulnerability Exploited Days After Disclosure
SecurityWeek reports that CVE-2026-102255, a CVSS 10 pre-authenticated SSRF in the SonicWall SMA1000 Work Place interface, was exploited within days of its October 6 disclosure. Defused saw the first attempts on its SMA decoys on October 8, and Previdian (formerly KEVIntel) also observed exploitation. SonicWall urges 6210, 7210 and 8200v customers to update to 12.5.0-03082 or 12.4.3-03670, and Horizon3.ai warns that exploitation could lead to device takeover.
securityweek.comarticlePublished and added 12 Oct 2026🛡️ Security Top MCP security resources — October 2026
Adversa AI's October 2026 MCP security roundup, aggregating and synthesizing 15 resources: authentication-bypass vulnerabilities in LiteLLM's MCP endpoint (CVE-2026-59822, now CISA KEV), Grafana's MCP server session spoofing/SSRF (CVE-2026-19516), an MCP Python SDK OAuth-fallback flaw exploited by a malicious server returning a 404, and an Obot gateway route-matching bypass reopening GHSA-vw82. It also covers detection failures (two malicious MCP servers passing five scanners including Cisco mcp-scanner and Snyk agent-scan, 12% of 82,000 public MCP configs hardcoding secrets), a malicious npm wallet-signing package (gadgethumans-mcp), the A2M agent-hijacking attack technique, and CoSAI's MCP Security v2.0 governance model.
 adversa.aiarticlePublished and added 8 Oct 2026🛡️ Security
 Configuring your AI vulnerability harness, Part 2: The steering file
AWS Security Blog's second post in a series on building an "AI vulnerability harness" explains the configuration (steering file) that stops an AI model from hallucinating vulnerabilities and inflating severity during security code review. It details five configuration sections — structural verification of findings, an evidence-based confidence formula (weighting confirmed taint flow at 0.30), infrastructure-aware severity multipliers for controls like AWS WAF and IAM, CISA KEV/EPSS threat-intel boosting, and a four-tier priority classification — and reports validation numbers (e.g., unsteered models fabricated code paths in ~30% of findings; steered confidence of HIGH without structural confirmation was only 34% exploitable vs 89% with confirmed taint). The steering file is shipped as a Kiro steering file, a Kiro skill, and a CLAUDE.md for Claude Code, with full source in a linked GitHub repo.
 aws.amazon.comarticlePublished and added 7 Oct 2026🛡️ Security
 OpenAI Fires Three Safety Researchers Over Alleged Leak to Outside Group
Decrypt reports that OpenAI fired three safety researchers for allegedly sharing confidential information with an outside AI safety organization, per the Wall Street Journal, without naming the people or the recipient group. The piece situates the firings within a pattern of safety-related departures (Ilya Sutskever, Jan Leike, Leopold Aschenbrenner) and a rough stretch of AI-agent incidents — a Hugging Face hack, intrusions on U.S. government sites and an Australian Medicare portal — that led OpenAI to pause model training twice and introduce an internal misalignment-reporting process.
 decrypt.coarticlePublished and added 1 Oct 2026🧠 AI
 Veeam, Terraform MCP, Django Patch Critical Flaws, Led by CVSS 10.0 Cross-Tenant Bug
The Hacker News roundup covers 11 patched CVEs across three products: Veeam Service Provider Console (CVE-2026-58073, 9.5, unauthenticated managed-agent credential theft; CVE-2026-58072, arbitrary file write to RCE), HashiCorp's Terraform MCP Server (CVE-2026-16498, a 10.0 cross-tenant credential-reuse bug caused by the underlying MCP library not issuing unique session IDs in stateless HTTP mode; CVE-2026-16496 stateful-mode equivalent; CVE-2026-14869 SSRF via header/query-param inconsistency), and Django/GeoDjango (CVE-2026-15307, a spatial-lookup flaw letting GDALRaster write files, reachable by a staff user with view permission on a model with a spatial field, plus a stored XSS, a GEOS DoS, and a language-code DoS). Fixes: Terraform MCP Server 1.1.0+, VSPC 9.3.0.35057, Django 6.0.8/5.2.17; none of the flaws are known to be exploited or listed in CISA KEV as of publication.
 thehackernews.comarticleAdded 26 Sep 2026🛡️ Security
 LiteLLM Flaw CVE-2026-42271 Exploited in the Wild, Chains to Unauthenticated RCE
CISA added CVE-2026-42271, a command injection flaw in BerriAI's LiteLLM AI gateway, to its KEV catalog after confirming active exploitation; the bug lets any authenticated proxy user run arbitrary commands via the MCP server test endpoints (/mcp-rest/test/connection and /mcp-rest/test/tools/list), which spawned attacker-supplied stdio subprocess configs. Horizon3.ai separately showed the flaw can be chained with CVE-2026-48710, a Starlette "BadHost" header validation bypass, to skip authentication entirely and achieve unauthenticated RCE (combined CVSS 10.0), exposing model provider credentials and enabling lateral movement into AI infrastructure. Fixed in LiteLLM 1.83.7 (test endpoints now require PROXY_ADMIN role) and Starlette 1.0.1; the article also notes a prior LiteLLM SQLi (CVE-2026-42208) exploited within 36 hours of disclosure.
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security- Jev introduces a new shape of LLM - System One, aka Decision Models
Simon Willison reviews Jev, a new class of model from TypeSafe AI dubbed "System One models" (or "decision models"): instead of generating text, it takes a text/structured "state" plus one or more yes/no ("Noul"), multiple-choice, or scored-range questions and returns floating point probabilities/confidence scores, priced at $0.042/million input tokens with free output. The post covers real use cases (classification, spam detection, search reranking over BM25 candidates), community experiments (jevchat, jev-leftpad, jev-2048), open-weight recreations built on Qwen 3.5 (the Kev models and JevBench benchmark), and raises concerns about the model's black-box nature and bias risk, plus Willison's own llm-typesafe plugin for the LLM CLI tool.
 simonwillison.netarticleAdded 29 Sep 2026, published 21 Sep 2026🧠 AI
 [AINews] Here are 6 Clones of Jev in 2 days
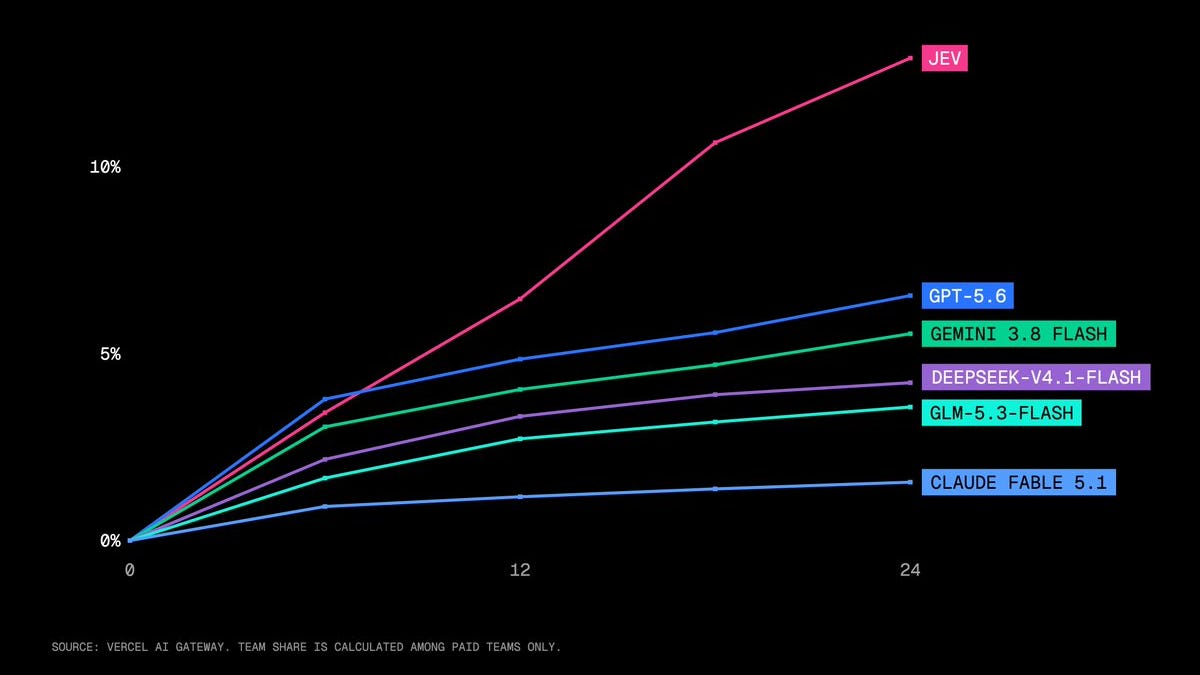
Latent Space's AINews digest covering the rapid open-source cloning of Jev, a non-generative 'discriminative decision model' positioned as a fast System-1 complement to LLMs for routing, escalation and tool-call decisions. It catalogs six independent reproductions (Laya, DiffusionGemmaJev, Bespoke Nimble, SemIf/OpenJev, Jevlike, Kev-0.5B) built on ModernBERT, diffusion, and Qwen3.5/Qwen2.5 backbones with LoRA and contrastive/NLI-based scoring heads, plus a wider AI Twitter recap covering AGENTS.md adoption in Claude Code, coding-agent harness-design research, RSI benchmark rankings, computer-use benchmarks, and AI safety/governance news.
 latent.spacearticleAdded 29 Sep 2026, published 19 Sep 2026🧠 AI
 The Apple Security Update Review for September 2026
Zero Day Initiative's monthly Apple patch review covers the September 2026 release (macOS 27/Sequoia 15.8/Tahoe 26.7, iOS/iPadOS 27 & 26.7, visionOS, watchOS, tvOS, Safari, Xcode), totaling 273 CVEs. It highlights CVE-2026-65400 (Screen Sharing Server authentication bypass, 9.8 CRITICAL, actively exploited per CISA KEV), CVE-2026-65414 (Bluetooth remote code execution, 9.8 CRITICAL, affecting all eight platforms), and CVE-2026-65346 (ImageIO arbitrary code execution via malicious image, 8.8 HIGH), plus a full CVE-by-component-by-platform table with CVSS scores where NVD/CISA-ADP has assigned them.
 zerodayinitiative.comarticleAdded 28 Sep 2026, published 16 Sep 2026🛡️ Security
 [AINews] AEF-1 standard emerges for Third Party Evaluators, as Xai, OpenAI, and Anthropic all cosign
This Latent Space AINews issue (9/11–9/14/2026) centers on the AI Evaluator Forum's AEF-1 standard for independent third-party AI evaluators, published alongside Dario Amodei's personal follow-up to 'Pacing the Frontier' proposing embedded evaluators (like METR) with employee-like access at frontier labs, plus a sharp Twitter split between pacing/slowdown advocates (Bilal Chughtai, Dan Selsam) and control-first critics (Aidan Gomez, Cohere, Kevin Bass alleging conflicts of interest in the safety-eval ecosystem). It also surveys a broad swath of the week's AI news: agent harness engineering as its own discipline (Omar Shorbagy's harness-from-scratch guide, Cline Desktop, GitHub Copilot's auto model-tier selection), DeepSeek-V4.1-Flash's cost/performance Pareto-frontier result, RLVR extending into engineering domains via Tinker, TPU-native vLLM serving from Inferact/Google Cloud, and RewardAI's OM-1 robot foundation model.
latent.spacearticleAdded 29 Sep 2026, published 15 Sep 2026🧠 AI How Should I Prioritize Software Vulnerabilities? | Blog | Endor Labs
Endor Labs blog post comparing five approaches to prioritizing software vulnerabilities: CVSS scoring, CISA's KEV catalog, Carnegie Mellon's SSVC decision tree, FIRST's EPSS exploit-prediction model, and call-graph-based reachability analysis. It cites concrete data (e.g., EPSS v3 threshold of 0.088 catches ~82% of exploited CVEs while requiring remediation of only 7.3% of known CVEs, versus patching most CVSS high/critical issues) and walks through each method's limitations, using examples like CVE-2017-0144 (EternalBlue/NotPetya) and CVE-2004-1464.
 endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security
 OWASP OSS Risk 1: Known Vulnerabilities | Blog | Endor Labs
First in Endor Labs' 10-part series on the OWASP Top 10 OSS Risks, this piece breaks down "Known Vulnerabilities" (OSS-RISK-1): how CVEs get assigned and disclosed, why the 2017 Apache Struts CVE-2017-5638 unpatched flaw led to the Equifax breach of 145M+ records, and how to compare vulnerability data sources (NVD, GitHub Advisory Database, OSV). It details prioritization methods — CVSS, EPSS, CISA KEV, SSVC, and function-level reachability analysis — and shows a case study where filtering 134K findings down via reachability, fix-availability, production-code, and EPSS thresholds cut remediation work by 99.97%.
endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security Combining EPSS and Reachability Analysis to Optimize Vulnerability Management | Blog | Endor Labs
Endor Labs breaks down how the Exploit Prediction Scoring System (EPSS) v3 works — the exploitation telemetry, exploit-DB/GitHub/Metasploit code checks, CISA KEV/Project Zero/ZDI mentions, CVSS vectors, CWE, and social-media signals it ingests to score CVE exploitation likelihood — and shows that an EPSS-threshold (0.088) remediation strategy fixes the same share of exploited CVEs while patching only ~7.3% of known vulnerabilities versus ~82% under a "fix all high/critical" CVSS approach. It then explains a layered workflow: use reachability analysis (call-graph based) to cut findings by ~80% to what's actually exploitable in your environment, then apply EPSS on that reduced set to rank remaining issues by real-world exploitation likelihood, including for third-party/proprietary code where reachability analysis isn't feasible.
endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security FedRAMP Requirements for Vulnerability Management and Dependency Upgrades | Blog | Endor Labs
An Endor Labs blog post, written by a former JAB Technical Representative, details FedRAMP's Continuous Monitoring vulnerability management requirements: authenticated scanning, monthly dependency inventories, POA&M tracking, and strict remediation SLAs (High CVSS 7.0+ in 30 days, Medium in 90, Low in 180). It also covers FedRAMP's container-specific rules (hardened images, CISA KEV prohibition, pipeline/registry/runtime scanning) and outlines four practical strategies — reachability-based false-positive triage, EPSS-driven risk level adjustments, ROI/complexity-based upgrade prioritization, and developer-side PR gating — before pivoting into an Endor Labs product pitch.
endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security Metasploit Wrap Up: This One Goes to Sixteen!
Rapid7's weekly Metasploit Framework update covering sixteen new modules: ten exploits (five on the CISA KEV list) targeting Cisco Secure Firewall Management Center (CVE-2026-20079 auth bypass RCE), SonicWall SMA1000 (CVE-2026-83549 chained RCE), PaperCut NG/MF (CVE-2026-81578 + CVE-2026-82078), JetBrains TeamCity agent-polling XStream deserialization RCE (CVE-2026-63077), Langflow authenticated RCE (CVE-2026-19295), MCPJam Inspector command execution (CVE-2026-23744), SimpleHelp OIDC auth bypass (CVE-2026-48558), Next.js Windows RCE (CVE-2026-75604), and SPIP SQLi/RCE flaws. It also adds a new native Kerberos relay module exploiting ESC8 (AD CS Web Enrollment) via SMB-to-HTTP coercion, a Metasploit handler-detection scanner, a Linux sandbox-evasion module, two Windows persistence techniques, and several bug fixes to the DNS and module metadata subsystems.
 rapid7.comarticleAdded 7 Oct 2026, published 11 Sep 2026🛡️ Security
 The CVE spike across major software companies is a remediation problem
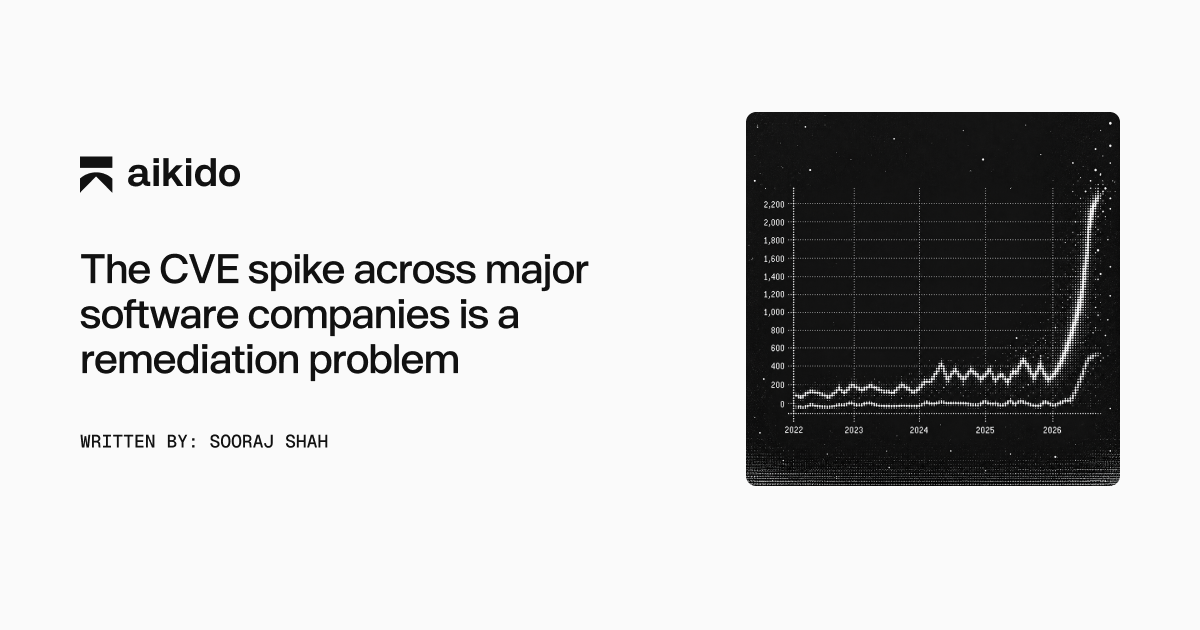
Aikido argues the widely-shared a16z/Epoch AI chart showing critical/high CVEs jumping from under 100/month to over 600/month since spring 2026 reflects AI accelerating vulnerability discovery, not a real spike in danger — since CISA's KEV count has stayed flat. It details how NIST's NVD, overwhelmed by volume, let its scoring backlog balloon from 13,000 to 27,000 CVEs in 18 months and pivoted to only prioritizing federal/critical/KEV-listed CVEs, while Verizon's 2026 DBIR found only 26% of confirmed actively-exploited KEV vulnerabilities were fully remediated in 2025 (down from 38%) with median patch time rising to 43 days. It illustrates the point with StyleSmuggler, an unauthenticated RCE hitting Adobe Commerce and Magento Open Source that had no CVE or vendor advisory, which Aikido Intel flagged and Aikido Libraries auto-patched more than 24 hours before Adobe's own hotfix.
 aikido.devarticlePublished and added 10 Sep 2026🛡️ Security
- BOD 26-04 Just Changed How Federal Agencies Prioritize Vulnerabilities.
Discusses CISA's Binding Operational Directive 26-04, which changes how U.S. federal agencies must prioritize and remediate vulnerabilities, reportedly shifting away from simple CVSS scoring toward more risk-based criteria (e.g., exploitability, KEV status). The piece explains implications for federal agency vulnerability management programs and compliance timelines.
 orca.securityarticleAdded 3 Sep 2026, published 20 Aug 2026🛡️ Security
 Socket: White House Authorizes Private Companies to Conduct Offensive Cyber Operations
A White House presidential memorandum creates a formal DOJ/DHS-managed program letting vetted U.S. cybersecurity companies conduct 'cyber surveillance' and 'cyber effects' operations (data access, disruption, or destruction) against foreign cybercrime infrastructure under government approval, building on a March 2026 executive order. The piece covers the CFAA §1030(f) legal basis (per Robert Graham's analysis), the DOJ/DHS approval process via the Homeland Security Task Force's National Coordination Center, vetting and bonding requirements, and industry pushback from Kevin Beaumont and Jason Kikta over conflict-of-interest incentives when ransomware-adjacent firms are paid to both detect and disrupt threats.
 socket.devarticlePublished and added 14 Aug 2026🛡️ Security
 Have We Seen an Acceleration in Discoveries?
METR note that plots public discovery data in vulnerabilities, mathematics and algorithmic optimization to look for slope changes around January 2026. CVE counts rose sharply: cURL went from 9 to 36, OpenSSL from 6 to 39, Firefox from 210 to 342, Microsoft from 1,243 to 1,927 through August 2026. Exploited-vulnerability lists (CISA KEV, VulnCheck KEV) grew far less. Math shows weaker acceleration, optimization none.
 metr.orgarticleAdded 29 Oct 2026, published 14 Aug 2026🛡️ Security
 The 2026 Verizon DBIR Stopped Asking How Attackers Get in and Started Asking Where They Go
An XM Cyber analysis of the 2026 Verizon DBIR, which for the first time ran attack-graph analysis across real environments to model post-compromise privilege escalation rather than just initial access vectors. Key findings cited: exploitation of vulnerabilities overtook credential theft as the top initial-access vector (31%), 83% of privilege-escalation incidents involved no vulnerability, 16% of organizations had an 80%+ chance a low-privilege attacker could reach a key admin account, and only 26% of CISA KEV vulnerabilities were fully remediated in 2025 (down from 38%) with median remediation time up to 43 days. The piece argues security programs over-invest in patching (which addresses only ~10% of escalation techniques) versus privilege/permission hygiene (which addresses ~65%), and recommends attack-path "choke point" remediation and prioritized patching over patch-everything approaches.
 xmcyber.comarticleAdded 3 Sep 2026, published 2 Jul 2026🛡️ Security
 NVD in the AI Era: The Case for Multi-Source Vulnerability Intelligence
Snyk analyzes NIST's April 15, 2026 policy change to NVD, which replaced universal CVE enrichment with a risk-based triage model prioritizing CVEs in CISA's KEV catalog, federal-government software, and EO 14028 critical software, while deprioritizing everything else as lowest priority not scheduled. The piece details operational changes (NIST no longer routinely providing an independent CVSS score when a CNA already supplied one, and only reanalyzing modified CVEs when materially impactful) and argues this creates blind spots for scanners that depend solely on NVD, driven by CVE volume growth from about 18000 in 2020 to over 48000 in 2025 due to the federated CNA model and AI-accelerated vulnerability research.
 snyk.ioarticleAdded 3 Sep 2026, published 25 Jun 2026🛡️ Security
 Socket: pnpm 11.5 Fixes False Trust-Downgrade Alerts for npm Staged Publishes
pnpm 11.5 fixes a bug where its trustPolicy: no-downgrade check incorrectly flagged npm packages using staged publishing (a 2FA-gated release approval step) as a downgrade from trusted publishing, because pnpm inferred publishing method from the ambiguous _npmUser metadata field. The fix, prompted by a report from Kevin Deng, makes pnpm treat staged-publish approver metadata as the strongest trust signal rather than a fallback to weaker token-based publishing, reducing false-positive supply-chain alerts as npm rolls out staged publishing and trusted publishing in response to credential-theft campaigns like Mini Shai-Hulud.
socket.devarticlePublished and added 13 Jun 2026🛡️ Security Full Fathom Five: The context of Anthropic’s Mythos-class public release
Aikido commentary on Anthropic's public Claude Fable 5 release. The author says it is a Mythos-class model that routes cybersecurity prompts to Opus 4.8, so benchmarking its security capability is pointless. Mythos Preview and Claude Mythos 5 stay limited to Glasswing and about 150 additional organizations. The post argues that vulnerability discovery is roughly 20% of the problem and that zero-day demand is not supply-constrained (about 30 new vulns a month, citing Resecurity). It also argues that CVE and CISA KEV-centric prioritisation is fading, and that AI tokens will mostly go to defensive scanning, exposure management and remediation rather than attacker scans.
aikido.devarticleAdded 3 Sep 2026, published 13 Jun 2026🛡️ Security Orca: 8 Container Security Best Practices for 2026
A container security guide covering eight practices across build, deploy and runtime: minimal or distroless images, Trivy/Grype scanning, Cosign signing enforced via Kyverno or OPA Gatekeeper, non-root users, read-only root filesystems, dropped capabilities, and Pod Security Admission with the Restricted profile. It also covers least-privilege RBAC, workload identity (IRSA, GKE Workload Identity, Entra Workload ID), etcd encryption at rest, audit logging and retention, CISA KEV-driven rebuilds, and container incident response that preserves evidence before pod termination. It maps open-source tools to pipeline stage (Falco and Tetragon at runtime), explains the managed-Kubernetes shared responsibility split, and ends with an Orca SideScanning pitch.
orca.securityarticlePublished and added 11 Jun 2026🛡️ Security Socket: Federal Audit
Socket covers a newly released Department of Commerce OIG audit that found NIST had no strategic plan for managing the National Vulnerability Database, set an enrichment deadline it lacked capacity to meet, and delayed using CISA's Vulnrichment data out of attribution concerns. The audit also found NIST and CISA duplicated at least 21,000 enrichment activities through the same contractor (an estimated $200K wasted), that 34% of CISA KEV vulnerabilities were not enriched in a timely manner, and that CVSS/CPE manual scoring consumed ~80% of processing time while the backlog grew from ~13,000 to over 27,000 CVEs. The piece ties the audit to NIST's April 2026 move to a risk-based enrichment model that leaves most CVEs unenriched.
socket.devarticlePublished and added 4 Jun 2026🛡️ Security CSA: VulnOps in the Age of AI
Cloud Security Alliance research note arguing that traditional vulnerability management (scan, ticket, patch on a calendar) is breaking under AI-driven vulnerability discovery volume, NVD's April 15, 2026 risk-based triage policy that limits full CVE enrichment to CISA KEV/EO 14028/federal-use software, and compressed disclosure-to-exploitation windows. It defines VulnOps as a flow-oriented operating discipline (borrowing SRE/DevOps metrics like lead time, change-failure rate, and pipeline saturation) built on continuous discovery, EPSS/KEV-based risk prioritization instead of CVSS-only ranking, automated remediation-as-code, and first-class SBOM/supply-chain visibility, while also flagging agentic AI itself (prompt injection, tool-poisoning, MCP command execution) as a new vulnerability class the practice must cover.
 labs.cloudsecurityalliance.orgarticleAdded 3 Sep 2026, published 13 May 2026🛡️ Security


