- Prasenjit Sarkar (@stretchcloud) on X
Campfire is a free, open-source, self-hosted tool that runs Claude Code, Codex, Goose, Aider and OpenHands side by side in one browser tab. Each agent gets its own git worktree, with permission voting (30 second timer, majority rules), session replay, cross-backend agent races and a shared semantic memory layer. Installs with bunx the-campfire. The post also compares Clawboo, Conductor, Vibe Kanban and Crystl.
 x.comthreadAdded 1 Nov 2026, published 31 Oct 2026🧠 AI
 Pre-ERC: Agent Pre-Sign Risk Report
 is a draft Ethereum Magicians proposal for an EIP-712-signed report that a risk source, identified by an ERC-8004 identity, returns about one unsigned request. It carries typed findings on tokens, approvals, addresses, payments (x402) and texts, and each finding is marked read or not read. It has no score or verdict, so the consumer applies its own policy. The author's live implementation, toll, runs on Robinhood Chain.
 ethereum-magicians.orgthreadPublished and added 31 Oct 2026🛡️ Security
- 🚨 AI News | TestingCatalog (@testingcatalog) on X
RoboAPI is a public API from PokeBot, powered by its world-action model Poke-Aurora, that lets robot arms do new tasks from natural-language instructions with no task-specific data collection or training. A user connects a supported arm with a wrist-mounted camera, gives a task such as "clean the table", and receives the next moves in near real time. The post gives no benchmarks, supported hardware list or pricing.
x.comthreadAdded 1 Nov 2026, published 31 Oct 2026🧠 AI - Anthropic Cracking Down on Video Game Rewrites
A tweet from chasmmmmmmmmmmm says Claude Code received a new rule around 27 October 2026, delivered from Anthropic's servers under the flag "tengu_heron_brook", with no setting to disable it. The quoted rule allows original games, genre games and games from the user's own designs and assets, but forbids recreating a specific existing game, even if renamed. The post asks whether this ends game rewrites and modding, and gives no verification beyond the quoted text.
 twitter.comthreadAdded 31 Oct 2026, published 30 Oct 2026🧠 AI
- Backdoors in official Claude Code extensions
GossiTheDog's Mastodon post reports that the Anthropic Claude Code Visual Studio extension, as installed in Cursor, contains malware that creates a remote access Trojan on desktops. It links to a phorion.io blog post on the reported compromise of the official Claude Code VSX extension. The post gives no technical detail, indicators or dates itself.
 cyberplace.socialthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
 Shubham Mishra 🐐 (@shubh6200) on X
A post relaying Cursor's security advisory: a modified, malicious Claude Code VS Code extension was distributed through the Cursor extension marketplace, affecting at most 5,000 users. Anthropic did not develop that version, and other extensions are not affected. Users of Claude Code in Cursor are told to update to version 2.1.314. The post adds that marketplaces need publisher verification and package integrity checks. It gives no technical detail on the payload.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security Trail of Bits (@trailofbits) on X
Trail of Bits post on X summarising Binance's initial investigation into a security incident. Binance suggests a compromised DevOps engineer's laptop let an attacker reach a service container and submit unauthorized withdrawal transactions. The text says no evidence has been found of wallet private key compromise. The fetched text is truncated and gives no further detail.
x.comthreadPublished and added 30 Oct 2026🛡️ Security- aiproduck (@aiproduck) on X
Ruflo is an MIT-licensed wrapper for Claude Code and Codex that adds agent swarms, vector memory and an MCP server. The plugin install writes no files to the workspace, while npx init adds a .claude/ directory, CLAUDE.md and hooks. The post warns that mods run with the account's permissions, so users should read them first. It gives no benchmarks or architecture detail.
x.comthreadPublished and added 30 Oct 2026🧠 AI  Rohan Paul (@rohanpaul_ai) on X
Rohan Paul's X post summarizes a TikTok paper on MCP attacks. LLM agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the user query, the server reply and the final answer. The attack works because agents read natural-language tool descriptions when choosing and ordering tool calls. The visible text is truncated and gives no success rates or defenses.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security- 🚨 AI News | TestingCatalog (@testingcatalog) on X
Mistral Large 4 ("Le Chonk") is an open-weights model from Mistral, now on Hugging Face. Per Mistral's announcement quoted in the post, it ranks #1 among open models on Cognition's FrontierCode benchmark, is aimed at agentic coding and cybersecurity, and claims better reasoning efficiency and lower inference costs. The post does not give parameter counts, license or benchmark scores.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI  SGLang (@sgl_project) on X
SGLang announces Day-0 support for Mistral Large 4 ("Le Chonk"), saying it is the first engine to serve the model on NVIDIA Vera Rubin. The post describes the model as Mistral's largest to date: a natively multimodal 1T-parameter mixture-of-experts model covering instruct, reasoning, coding and agentic workflows. The fetched text is truncated, so benchmark claims and launch commands are not visible.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI Muhammad Waris (@WarisCodes) on X
Nemotron 3.5 Transcribe is a free open-weight speech-to-text model from NVIDIA covering 40 languages, including mixed-language speech. The post says it ties for first among open models with a 2.8% error rate. It says the model needs a large GPU such as an H100 or RTX 5090, so it will not run on a laptop. The post gives no benchmark name or model card link.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI- 🚨 AI News | TestingCatalog (@testingcatalog) on X
Nemotron 3.5 Transcribe is an open-weight, promptable NVIDIA mixture-of-experts model with 30B total and about 4B active parameters. One checkpoint does transcription in 40 languages, speaker attribution, translation, contextual prompting and audio understanding. The post says it ranked first in VoiceArena's comparison of 14 diarization plus ASR systems. The fetched text is cut off and gives no license or download details.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI - Dark Web Intelligence (@DailyDarkWeb) on X
DailyDarkWeb post summarising Anthropic Frontier Red Team research published 27 October 2026. An unreleased internal Claude research model built five attack chains: Chrome sandbox escape (V8 heap bug, CacheStorage race, FedCM use-after-free), a Safari same-origin policy bypass, data extraction from a locked Pixel 9 over USB, a Windows QUIC kernel crash (CVE-2026-33096) and zero-click Linux root via multipath TCP (CVE-2026-98432). Anthropic says all flaws are fixed, including 62 Chrome CVEs as of Chrome 156. The post notes the chains are not independently reproduced.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security - Rohan Paul (@rohanpaul_ai) on X
Rohan Paul's X post summarizes the paper "Log-To-Leak: Prompt Injection Attacks on Tool-Using LLM Agents via the Model Context Protocol", from TikTok researchers. It reports that MCP-using agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the query, server reply and final answer. The attack works through natural-language tool descriptions that agents read when choosing and ordering tools. The visible text is truncated.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security - Trail of Bits (@trailofbits) on X
Trail of Bits post says it achieved remote code execution through a Brotli decoder bug in Linux lab setups: Node.js 24.22.0 with Express 5.3.0 via the standard JSON parser (x86-64 and ARM64), and Electron 41.10.7 (x86-64) with a custom decoding service. Exploitation needs a carefully matched setup and repeated attempts. A scanner by ToBScottA finds hidden copies of the decoder, including in stripped binaries.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security  TENSA Engineering (@TENSAEng) on X
A post by TENSAEng describing a workflow for staying within coding-tool usage limits. ChatGPT chat sits outside those limits, while Claude and Grok chats share a pool with Claude Code, Codex and Grok Build. Architecture, file layout, step order and acceptance checks are planned in ChatGPT and saved as repo docs. Claude Code or Codex then implements one small chunk per fresh session.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI- Laban (@lunkertw) on X
An X post summarising five AI items: Google DeepMind's Gemini 4 Carbon (88.2% SEC-bench Pro, 54.8% ExploitGym, 71.0% CWE-bench, 59 on Artificial Analysis Intelligence Index v5.0), Ed Zitron's critique of Anthropic's S-1, a Utah Claude Code pilot, and the repos beenuar/AiSOC and expo/skills. In the Utah pilot, 34 developers in 10 agencies took part over four weeks, 80% had a working setup within 30 minutes, and 71% saved over 20 hours. It gives short summaries and links, not primary analysis.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI - Niko (@nikolayxyz) on X
Gemini 4 Carbon is Google's new frontier model, announced in a post by nikolayxyz that quotes Google's launch text. It ranks #1 on v5.0 of the Artificial Analysis Intelligence Index with 59 points, ahead of Opus 5.5 and GPT-6 Astra. Intro pricing is $2 input and $10 output per million tokens. Access starts for cyber defenders first, as Gemini 4 Argon's did. The captured text is cut off before the rollout details.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI  John Rood (@johnroodepic) on X
Nemotron 3.5 Transcribe is an open-weight, promptable 30B mixture-of-experts model from NVIDIA with about 4B active parameters, built for recorded audio. One checkpoint transcribes 40 languages, handles recordings up to an hour, labels up to eight speakers, translates, and answers questions about English audio. Weights and a demo are on Hugging Face. The post gives no benchmarks.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI- 🚨 AI News | TestingCatalog (@testingcatalog) on X
Gemini 4 Carbon is a new Google model, announced in a TestingCatalog post on X as taking first place on the Artificial Analysis V5 ranking. It is rolling out to cyber defenders first. Reported scores are 88.2% on SEC-bench Pro (finding vulnerabilities), 54.8% on ExploitGym (exploitation) and 71.0% on CWE-bench (patching). The post calls it a large step up from Gemini 4 Argon, released two weeks earlier. It gives no technical detail beyond these claims.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🧠 AI  JFrog Security (@JFrogSecurity) on X
JFrog Security announces research on CVE-2026-102479 in Vert.x, which skips validating the letter 'L' in header names and so accepts `Content-Xength` as `Content-Length`. JFrog Research chained this with a dangling-byte primitive to bypass reverse proxy socket validation. They demonstrate end-to-end response poisoning and session fixation behind real reverse proxies. The post links to a full writeup; the tweet itself gives no exploit detail.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security Kizuno18 (@Kizuno18) on X
Kizuno18's X post argues that the move from local stdio and Docker MCP servers to remote HTTP/SSE endpoints matures the Model Context Protocol in enterprise infrastructure. It lists three trade-offs: short-lived OAuth/JWT bearer tokens replace mounted admin credentials, deferred tool discovery avoids roughly 20k tokens of eager schema loading, and HCP Terraform enforces Sentinel/OPA policy, audit trails and approvals server-side. Opinion post with no benchmarks or code.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026🧠 AI- Prasenjit Sarkar (@stretchcloud) on X
Campfire is a self-hosted workspace by Prasenjit Sarkar that runs Claude Code, Codex, Goose, Aider and OpenHands side by side in one tab. Risky actions go through permission voting: a majority approves, any single deny blocks, and a 30 second timer ends the wait. Session replay shows which file or tool call triggered an action. The post cites Forever Security's report of a planted AGENTS.md. Codex followed it first time over 90% of the time and Claude Code about half the time. Try it with "bunx the-campfire".
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI - Prasenjit Sarkar (@stretchcloud) on X
Campfire is a self-hosted tool that runs Claude Code, Codex, Goose, Aider and OpenHands in one tab. Risky actions need permission voting (majority approves, any single deny blocks, 30 second timeout), and session replay traces which file or tool call triggered an action. The post cites Forever Security's finding that Codex followed a planted AGENTS.md instruction over 90% of the time and Claude Code about half the time. It also cites the February Cline release compromise via a poisoned GitHub Actions cache.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security  cubillas (@cubillas888) on X
The tweet relays Pillar Security research that opencode on Windows and WSL could run attacker-controlled code during remote MCP server OAuth sign-in. The fix shipped in opencode 1.18.33 on 28 September, with no advisory or CVE published. It advises users of remote MCP servers to update and review which servers they connect to. Technical details are not in the post.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security- AGTP (@AGTPinsights) on X
AGTP's X thread summarizes Meta's Muse Spark 1.3 Evaluation Report. Prompt injection was tested on Exponential Security Labs' RepoInject v1 and BrowserInject v1 and on Gray Swan's IPI Arena, with robustness said to be on par with GPT-5.6 Sol. It also covers chain of thought controllability evals, PostTrainBench under Loss of Control, and Handshake's pre-release human red teaming. It notes the Midas Project's criticism of Muse Wonder's missing safety report.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security - AGTP (@AGTPinsights) on X
Thread summarizing Meta's Muse Spark 1.3 Evaluation Report, the safety write-up for the model released on September 2, 2026. It covers prompt-injection results on Exponential Security Labs' RepoInject v1 and BrowserInject v1 and Gray Swan's IPI Arena, chain-of-thought controllability evals, PostTrainBench under Loss of Control, and Handshake's human red teaming. It also notes The Midas Project's criticism that Muse Wonder still has no safety report, and the Muse Spark Open rollout (816B total, 42B active parameters).
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🧠 AI - Trail of Bits (@trailofbits) on X
Trail of Bits post on PHP2Shell, an exploit that gives a shell on MediaWiki, Symfony, Laravel and phpBB. They confirmed it on pre-patch PHP 8.2 to 8.5. An update says it is production-grade: it works with stock php.ini-production, display_errors off, multiple workers, ASLR and load, on ARM64 and x86-64, and reaches root on Apache/mod_php and nginx/php-fpm. No CVE or technical root cause is given.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security - The SI Maximalist (@thesimaximalist) on X
The SI Maximalist posts on X that OpenAI says GPT-6.1 Terra matches GPT-6 Astra on Agents' Last Exam, OpenAI's test of workplace software tasks, at one tenth of the token price. The model is available in ChatGPT Work, Codex and the API. The post only relays OpenAI's claim and gives no benchmark scores, exact prices or method.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🧠 AI  Masoud (@dev3mike) on X
Tweet from dev3mike warning Node.js users to update for CVE-2026-111497, a Brotli bug rated CVSS 9.2. Crafted compressed data can corrupt memory and possibly run code. The post says OpenAI's agents found it, and that the fix sat unreleased in Brotli's source since February. Patched versions are Node 22.23.4, 24.22.1 and 26.12.1.
x.comthreadAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security- TechNadu (@TechNadu) on X
TechNadu's post reports a hacker's claim of leaking 6 million records linked to CONAPE, the Dominican Republic's pension body. The alleged dataset includes national IDs, addresses, medical details and pension records. TechNadu notes that neither the records nor their link to CONAPE has been independently verified. The post gives no technical details on how the data was obtained.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security - Zex Alpha (@kryptozex) on X
Post about the "Steal My Bitcoin" bounty, a 0.025 BTC (about $2,025) prize that was swept early Monday, about 90 minutes after researcher @killa published a full exploit on GitHub. The exploit is a heap exploit written for the target's PHP build. It leaks memory addresses through session cookies and forces PHP cleanup to run the flag binary. The first solve looked like a failure because the pulled key did not control the advertised address, a planting mistake the creator admitted by email.
x.comthreadPublished and added 26 Oct 2026🛡️ Security - Ricardo Arguello (@RicardoIQSource) on X
Post by RicardoIQSource on breaches of developer platforms aimed at AI provider keys. It reports OpenCode (17 October, provider keys in its Console) and Zeabur (14-15 October, 3.2M environment variable records, admin tokens stored in plaintext since January 2024) as following the Railway incident. It claims three platforms were hit in eight days and links a blog with a timeline and remediation steps.
x.comthreadAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security - SemiAnalysis (@SemiAnalysis_) on X
SemiAnalysis claims AMD chips running vLLM can earn up to $3 per chip-hour in profit serving the open-source Kimi K3 model, even after higher chip rental prices following Claude Code's rise. Kimi K3 has over 2.8 trillion parameters and fits AMD's 288GB per chip, while B200 cannot hold it in one server. B200 must then use tensor or pipeline parallelism over 400Gbit/s InfiniBand or Ethernet, which SemiAnalysis says is 18x slower than NVLink. The post gives no methodology.
x.comthreadAdded 26 Oct 2026, published 25 Oct 2026🧠 AI - alex lee (@alexlee20122022) on X
Gheist is a GitHub campaign disclosed by Wiz in October 2026. Stolen tokens push ci-sync-XXXXXX branches with a sync-check workflow that dumps repo secrets base32-encoded to evade log masking, fetches the logs via API, then deletes the run. 13,500+ branches and 850+ accounts were hit since 15 September. Public repos are protected by the approval hold; private and Enterprise repos are not. The thread lists IOCs (.gdmp_pat files, "gheist" user agent, "ci: sync config" commits) and rotation steps.
x.comthreadAdded 26 Oct 2026, published 25 Oct 2026🛡️ Security - Draft ERC: Agent Safety Framework (ASF) — attributable adoption of versioned safety specifications
Agent Safety Framework (ASF) is a draft ERC (ethereum/ERCs pull request #2113) for an on-chain registry that records which participants adopted which versioned safety specification, for what subject and scope, and where it is enforced. It defines two objects (Safety Specification, Safety Binding) and a registry check returning Satisfied, NotSatisfied or Unknown. Two reference consumers and 73 tests (47 negative) are reported, and the post asks the community four design questions.
ethereum-magicians.orgthreadPublished and added 25 Oct 2026🧠 AI  su (@sutdmhy) on X
Kimi K3.1 Pro is a Moonshot AI model, with a high-speed variant, described in a tweet as a mixture-of-experts system of about 2.8 trillion parameters with a 1-million-token context window and multimodal support. The post claims gains in coding, long-horizon agents, 3D modeling (Blender/CAD) and financial research, and says benchmarks come close to Claude Opus 5.5. Full open weights are planned by November 4. The post gives no benchmark figures.
x.comthreadAdded 26 Oct 2026, published 25 Oct 2026🧠 AI- Gökdeniz Gülmez (@ActuallyIsaak) on X
An X post showing how to have Codex train a small model on Apple silicon through the mlx-lm-lora MCP server and skill. It gives five setup steps (pip install with the mcp extra, npx skills add, locate mlx-lm-lora-mcp, codex mcp add). The prompt runs four pre-training trials on tiny-random/qwen3 with the mlx-community/recycling_the_web-1k dataset. Codex picks the optimizer and learning rate itself, and the result is a table with validation loss and the best adapter path.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🧠 AI  Prasenjit Sarkar (@stretchcloud) on X
Post explaining Claude's new support for MCP Tasks and Elicitations. A server returns a durable task handle instead of blocking. The client polls tasks/get every 250 ms to 30 s, and states are working, input_required, completed, failed or cancelled. Elicitations pause a task at input_required for human approval. It also notes Cloudflare's stateless MCP servers and Code Mode, and Sentry and Linear adoption.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🧠 AI- The Hacker News (@TheHackersNews) on X
The Hacker News post relays LiteLLM's root-cause disclosure for its supply chain attack. A master key leaked on GitHub in May was never revoked. Attackers used it to reach the Agent Platform, steal a GitHub owner token, and publish a malicious PyPI release in October. A reply says the agent tool held the org owner's personal CLI login, which skips GitHub's 2FA re-check.
x.comthreadAdded 26 Oct 2026, published 24 Oct 2026🛡️ Security - Prasenjit Sarkar (@stretchcloud) on X
Post on the LiteLLM supply-chain compromise. Attackers spent eleven days in the GitHub org, ran a workflow on a throwaway branch to take twenty secrets including a GitHub App private key, then used stolen GitHub CLI OAuth tokens to publish malicious release 1.107.0 from a lookalike Berri-AI repo. A Python startup file harvested sixteen credential categories and LiteLLM proxy Postgres provider keys. Socket flagged the wheels in seven minutes.
x.comthreadAdded 26 Oct 2026, published 24 Oct 2026🛡️ Security  EveryDev.ai (@EveryDevAi) on X
ToolUniverse, from ScientistTools, is an open-source (Apache-2.0) toolkit that gives any LLM one interface to more than 1,000 scientific tools, models and databases such as PubMed, UniProt and ChEMBL. It ships a native MCP server, a Python SDK and a tu CLI, plus 68 pre-built agent skills. The post says it works with Claude Code, Cursor, Gemini CLI and Windsurf.
x.comthreadPublished and added 24 Oct 2026🧠 AI Hajrë Hyseni | AI for Business (@hajra) on X
Kimi K3.1 Pro is a new model from Moonshot AI. According to a post by hajra, Artificial Analysis ranks it 4th in the world, 3 points behind Claude Opus 5.5. The API price is down by a third, and full open weights are promised by 4 November. The post gives no benchmark breakdown, licence or architecture details.
x.comthreadPublished and added 24 Oct 2026🧠 AI- Big Bull (@BIGBULLapp) on X
A post by BIGBULLapp on X about a TensorBlock GitHub index of Model Context Protocol servers, described as a TypeScript list so agents call tools someone has already wired up. It cites 1470 forks, 943 stars and 15 open issues. The author notes that curated lists go stale when a server changes its schema. The repository name is truncated in the post.
x.comthreadAdded 24 Oct 2026, published 23 Oct 2026🧠 AI  Rafter (@RafterSecurity) on X
Railway security incident update of 23 October 2026, posted by Rafter Security, summarising Railway's preliminary report on the 20-22 October breach. Up to 1.85% of workspaces (about 100,000) may have had environment variables exposed. Attackers reportedly targeted AI provider API keys, possibly for model distillation. Some encrypted secrets were accessed and a subset decrypted. Railway says the attacker was removed by 22 October at 03:32 UTC, and the forensic investigation continues.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security- Previdian (@PrevidianCyber) on X
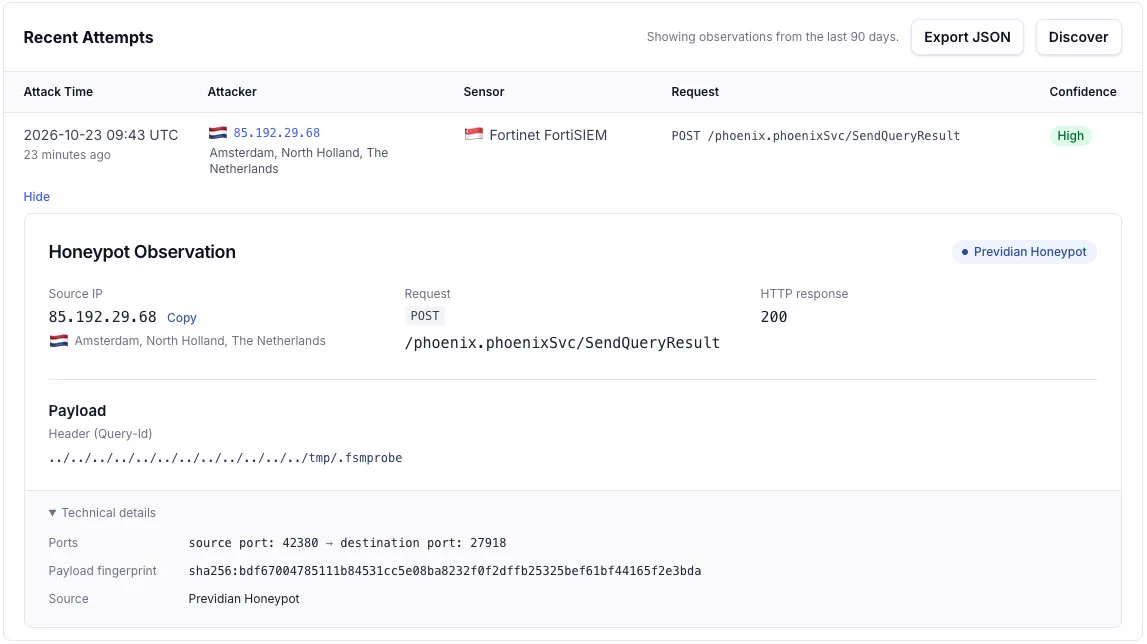
Previdian Cyber reports an exploitation attempt against its FortiSIEM honeypot on 23 October 2026 at 09:43:32 UTC, targeting the FortiSIEM path traversal CVE-2026-106173. The request, from 85.192.29[.]68, POSTed to /phoenix.phoenixSvc/SendQueryResult on TCP 27918 with twelve ../ sequences in the query-id header, trying to overwrite /tmp/.fsmprobe with an empty file. It matches the file overwrite mode of the Horizon3.ai PoC; success is not confirmed. Mitigation: upgrade to FortiSIEM 7.5.1 or later and restrict TCP 27918.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security - Techjunkie Aman (@Techjunkie_Aman) on X
ns2jb is a software-only jailbreak for the Nintendo Switch 2 running firmware 23.0.1, announced in a post on X. It runs arbitrary native code, allows save dumping, reverse engineering and game modding, and reaches most peripherals via MMIO. It is tethered (rerun after reboot) and gives no CFW or full kernel control. The post says Mario Kart World has been modded with custom characters. It gives no technical detail on the exploit chain.
x.comthreadAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
LiteLLM suspects its October 21 release compromise began with Claude Code responses containing GitHub CLI OAuth tokens that were written to logs of an internet-facing internal LiteLLM gateway. Attackers allegedly stole those tokens, used an organization-owner token to disable branch protections, and pushed poisoned artifacts from a lookalike repository. How they entered the gateway is unconfirmed, and this is not a proven Claude Code vulnerability.
x.comthreadAdded 25 Oct 2026, published 22 Oct 2026🛡️ Security - Muscle AI (@themuscleai) on X
Post on the LiteLLM 1.107.0 PyPI compromise published 21 October 2026 and quarantined about 1 hour 43 minutes later. A malicious .pth file ran at Python startup and stole cloud credentials, private keys, browser data and AI tool auth files, then POSTed a tarball to an attacker endpoint. The author says attackers used stolen GitHub CLI OAuth tokens to push a trojanized commit chain and build official wheels. It lists five defenses: hash-pinned lockfiles, per-tool capped keys, release cooling periods, secret isolation and egress monitoring.
x.comthreadAdded 23 Oct 2026, published 22 Oct 2026🛡️ Security  Jonathan Rhyne (@jdrhyne) on X
A post on X about NVIDIA's Nemotron 3.5 Parse and its "#1 on ParseBench" claim. The author says the ranking holds only among open-weight models under 1B parameters. On the full board of 150+ models the model scores about 75, while the top is near 90. The post asks vendors who run a benchmark to print the filter on the chart.
x.comthreadAdded 23 Oct 2026, published 22 Oct 2026🧠 AI Paul Dragoonis (@dr4goonis) on X
Social post summarising emergency patches for Node.js (4 high CVEs), PHP (2 critical) and nginx (3 critical). Node.js flaws include a Brotli decoder out-of-bounds write, a DNS truncation bug and two TLS hostname-verification bypasses. PHP has use-after-free and heap corruption bugs, and nginx has alias-rewrite and map-regex heap overflows plus an SSI-AIO use-after-free. It lists the fixed versions for each product.
x.comthreadAdded 23 Oct 2026, published 22 Oct 2026🛡️ Security- ERC-TBA: Agent Income Statements
ERC-TBA: Agent Income Statements is a draft Ethereum standard, a profile of the ERC-8004 Reputation Registry. A writer posts chained statements of what an agent's agentWallet received in one asset, with each incoming transfer a Merkle leaf, so lenders and buyers can verify earnings from x402 payments. Windows are cut at owner or wallet changes, and the post asks about statement grain, the MetadataSet requirement and who may write. The reference implementation is unaudited.
ethereum-magicians.orgthreadPublished and added 22 Oct 2026🧠 AI - Nagli (@galnagli) on X
Tweet by Gal Nagli (galnagli) saying a Gemini model turned the GitLab advisory for CVE-2026-110264 into a working heap exploit in 17 minutes, with the full chain done in about another hour. The flaw is a CVSS 10.0 unauthenticated RCE on self-managed GitLab servers, affecting 12 years of releases, found by joaxcar. The post links a The Hacker News article and gives no technical details of the exploit.
x.comthreadAdded 23 Oct 2026, published 22 Oct 2026🛡️ Security  SecureChap (@SecureChap) on X
Post describing a LiteLLM 1.107.0 PyPI compromise in which attackers used stolen GitHub CLI OAuth tokens from three engineers to trigger and approve the project-releaser workflow, producing eight malicious wheels and a tampered tarball. The wheels drop cook.pth, which runs at Python startup, and privcollect steals cloud tokens, keys, browser data, AI configs and LiteLLM proxy credentials, exfiltrating to litellm[.]dev/healthcheck. A second daemon polls a GitHub domain.txt hourly for new domains to fetch and execute. PyPI yanked the package the same day. The post is a single unsourced tweet.
x.comthreadPublished and added 22 Oct 2026🛡️ Security- elvis (@omarsar0) on X
FrontierMemory is a benchmark that evaluates agent memory through downstream task performance, measuring how agents learn from experience rather than recall, which the post says is saturated via agentic search. In elvis's summary, Claude Opus 5.5 ranks first and open-weight GLM-5.3 does well on memory generation. The authors reply that "memory" here means any adaptation from experience, so harness-level changes can also be scored. The post gives no scores or links.
x.comthreadAdded 23 Oct 2026, published 21 Oct 2026🧠 AI - Trail of Bits (@trailofbits) on X
Trail of Bits post on two unpatched critical PHP bugs that were exploited within 17 hours of details leaking. Cloudflare began blocking attacks and Patchstack reported active exploitation. The bug was reported 11 August and fixed 71 days later, with a patch touching 402 files and over 11,000 lines. Trail of Bits announces two open-source plugins, patching-bugs and regression-hunt, from its Patch the Planet work.
x.comthreadAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security  VibecodersHQ (@VibeCodrHQ) on X
Post summarising Pillar Security's finding of a remote code execution flaw in OpenCode, the open-source AI coding agent. Versions 1.0.137 through 1.18.32 could run code from a remote MCP server during OAuth sign-in on Windows and WSL, with no prompt injection needed. The fix is in 1.18.33 (released 28 September). No advisory or CVE was issued, so scanners will not flag old installs. Interim advice is to remove unvetted remote MCP servers.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security Open Weight Updates (@openweightstars) on X
Flint is the first model from Recursive SI, a fast local coding model with open weights released the same day. It was built with the company's automated research system, the Eureka Machine. The post claims up to 2x faster speed than comparable models: 125+ tokens/sec on a MacBook Pro and 150+ on RTX Spark. The captured text is truncated and gives no benchmarks or model size.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🧠 AI- Swif (@swif_ai) on X
Swif (@swif_ai) reports that in the MCP TypeScript server SDK versions 2.0 to 2.2, a single server instance shared by several HTTP clients, which is the pattern the README shows, could send one client's responses to another client. Version 2.3.0 refuses this setup, so developers must build a server per request or per session. The post gives no CVE, advisory ID or technical detail.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security - Swif (@swif_ai) on X
A post from Swif (@swif_ai) on the MCP TypeScript server SDK versions 2.0 to 2.2. A single server instance shared across HTTP clients, the pattern shown in the README, could send one client's responses to another client. Version 2.3.0 refuses that setup, so servers must be built per request or per session. The post gives no code or advisory ID.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🧠 AI - 0xMarioNawfal - The Roundtable Show (@RoundtableSpace) on X
TorchTPU is Google's open-source project for running PyTorch apps on its TPUs, announced the day after Amazon released TorchNeuron for its Trainium chips. Google says migration needs "a simple configuration change" with no rewrite. It worked with Meta, Hugging Face, and the vLLM and SGLang teams on compatibility, and added an agent suite that helps migrate apps and fix errors. The post is brief and gives no benchmarks.
x.comthreadAdded 21 Oct 2026, published 20 Oct 2026🧠 AI  brenz. (@brenzhills) on X
Krea 3 is an image generation and editing model from Krea. A post on X says its "Fast" variant scores 1125 Elo on the Artificial Analysis image editing leaderboard, against 1124 for Google's Nano Banana 2, while producing 10 images in the time Google produces 2. It also says the "Ultra" variant ranks in the top 4, behind only OpenAI models. The post gives no methodology or model details.
x.comthreadAdded 21 Oct 2026, published 20 Oct 2026🧠 AI Parul Gautam (@Parul_Gautam7) on X
Beacon is an open-source memory layer for coding agents. It saves sessions across Claude Code, Cursor, Codex and more than 20 other tools, so developers can move work between agents without losing context. The team says it raised a $5.5M seed round and is building a self-improving feedback loop that learns from how users debug. The post gives no technical detail or repo link.
x.comthreadAdded 21 Oct 2026, published 20 Oct 2026🧠 AI- ︎ (@0xocdsec) on X
Post from 0xocdsec announcing a deep-dive on CVE-2026-106173 in Fortinet FortiSIEM. The flaw is an arbitrary file write in a gRPC service that leads to remote code execution. The author says this is the fourth year in a row they have researched FortiSIEM. The post itself gives no technical detail and links to the full analysis.
x.comthreadAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security - Trail of Bits (@trailofbits) on X
Trail of Bits thread on Google Quantum AI's March publication of a new Shor's algorithm version aimed at secp256k1, the curve protecting Bitcoin and Ethereum wallets. Google used zero-knowledge proofs to keep the attack details secret, and the post says the secrecy lasted 63 days. The fetched text is cut off after the qubit estimate of roughly 1,200, so later details are missing.
x.comthreadAdded 22 Oct 2026, published 20 Oct 2026🛡️ Security - Pre-ERC: Adoption Profile and Reference Kernel for EOAs Adopting Code via SETCODEFROM
Pre-ERC proposal for EOAs that adopt account code via EIP-8298 SETCODEFROM, which with EIP-8151 retires the secp256k1 key. It lists seven failure modes (FM1-FM7), such as self-recovery lockout, ERC-1271 passing while VERIFY fails, front-runnable initialization and a mutable code source. It proposes requirements R1-R8, a MigrationCheck guard with two routes, and a reference kernel with post-quantum ERC-7913 verifiers.
ethereum-magicians.orgthreadPublished and added 20 Oct 2026🛡️ Security  Paulo Pierrondi | AI agents (@paulopierrondi) on X
Paulo Pierrondi's X post, part 9 of a series on installing MCP servers, lists a monthly review of installed servers. The checks are which tools the agent used, servers not called in weeks, overlapping tools that confuse the model, and whether each server still has an owner. A reply adds a decommissioning check: after removal, confirm the server's old credentials can no longer call the backend.
x.comthreadPublished and added 20 Oct 2026🧠 AI- DFIR Radar (@DFIR_Radar) on X
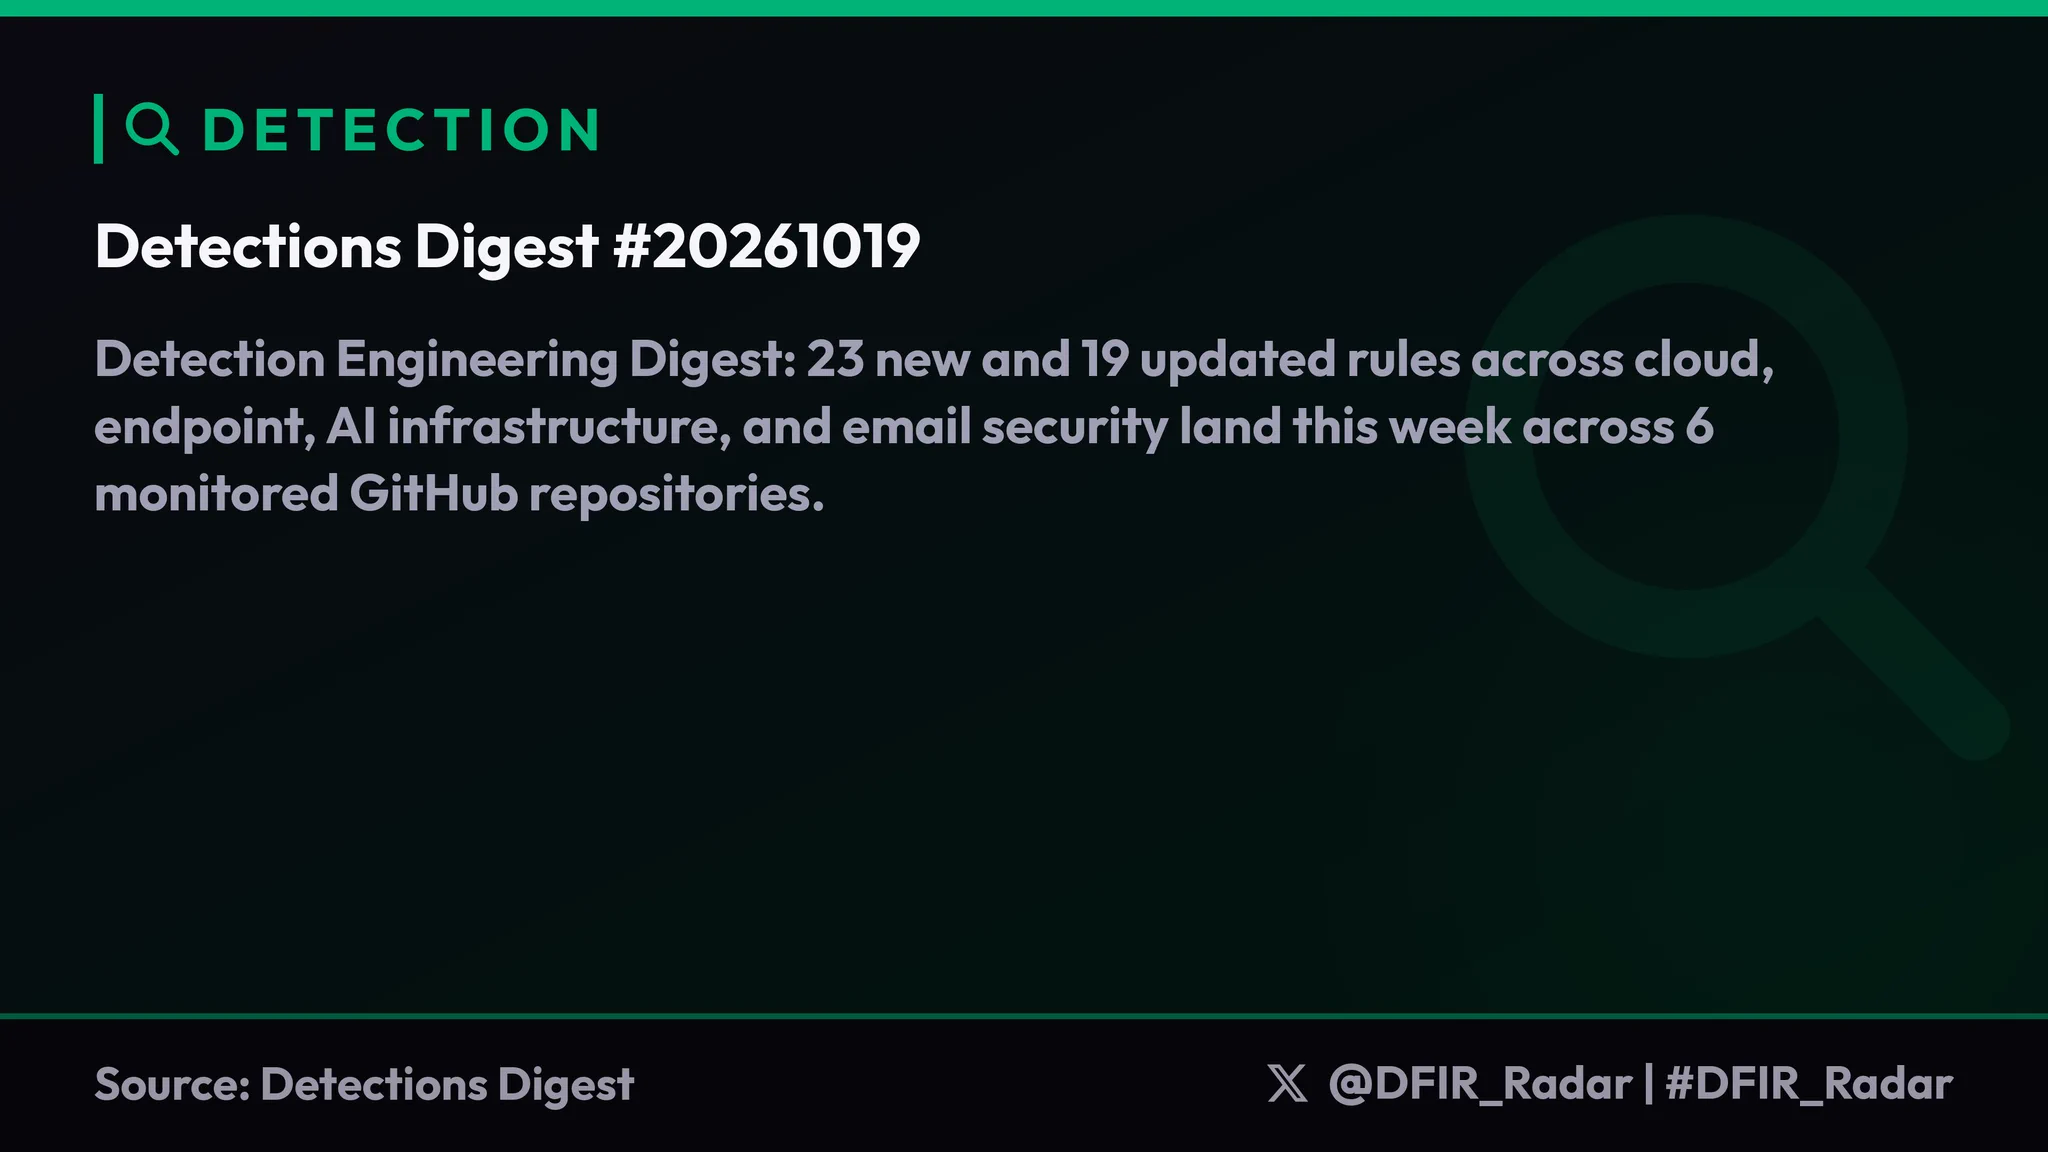
DFIR_Radar weekly detection engineering digest covering 23 new and 19 updated rules across 6 GitHub repositories. It lists KQL rules for Azure Key Vault secret retrieval, MCP client User-Agent bulk operations and local Azure token theft, AWS CloudTrail analytics, Sigma rules for firewall and ETW tampering (decimal 17 vs hex 0x11), updated LOLDrivers hashes, and Sublime email rules for OAuth consent phishing and fake IRS W-9 PDFs.
x.comthreadAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security  Nick Frichette (@Frichette_n) on X
Datadog Security Labs announcement, posted by Nick Frichette, of research on steering the evaluations of a prompt-injection detector called "Jev". The team's method cut its detection rate from about 83% to about 4% in their tests. They also used it to bypass LangChain's experimental tool-risk gating feature that is based on Jev. The tweet gives no method details and links to the full article.
x.comthreadAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security- LinuxSecurity (@lnxsec) on X
A post from lnxsec on CI runners that accept outside pull requests while also holding registry credentials, cache write access, signing material or deployment tokens. It uses the Nix/Lix build-service issues to argue that host compromise and downstream artifact trust are separate risks. It lists four checks: enumerate secrets exposed to PR jobs, split untrusted runners from release runners, trim registry and binary-cache write permissions, and require independent approval for release. It links a linuxsecurity.com feature; CVE details are not in the post.
x.comthreadAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security  Angel (@ziran_pu) on X
AshAi, the AI package for the Elixir Ash Framework, is getting MCP client tools. Creating an MCP server with AshAi was already simple, but connecting your own LLM tool loop to an external MCP server had to be built by hand. The planned release includes OAuth client management resources. The post gives no release date, API details or code.
x.comthreadAdded 21 Oct 2026, published 19 Oct 2026🧠 AI- Dark Web Intelligence (@DailyDarkWeb) on X
Plex2Shell is a chain of four Plex Media Server flaws (CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656) that a researcher says ends in unauthenticated RCE on servers older than 1.43.3.10861. A write-up and PoC were published on 16 October 2026. CISA advisory VA-26-266-01 scores the individual CVEs 4.3 to 7.2, and they are not in CISA KEV. The post advises updating, avoiding exposure of port 32400, and checking for unknown child processes and new files in the Codecs folder.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security - Dark Web Informer (@DarkWebInformer) on X
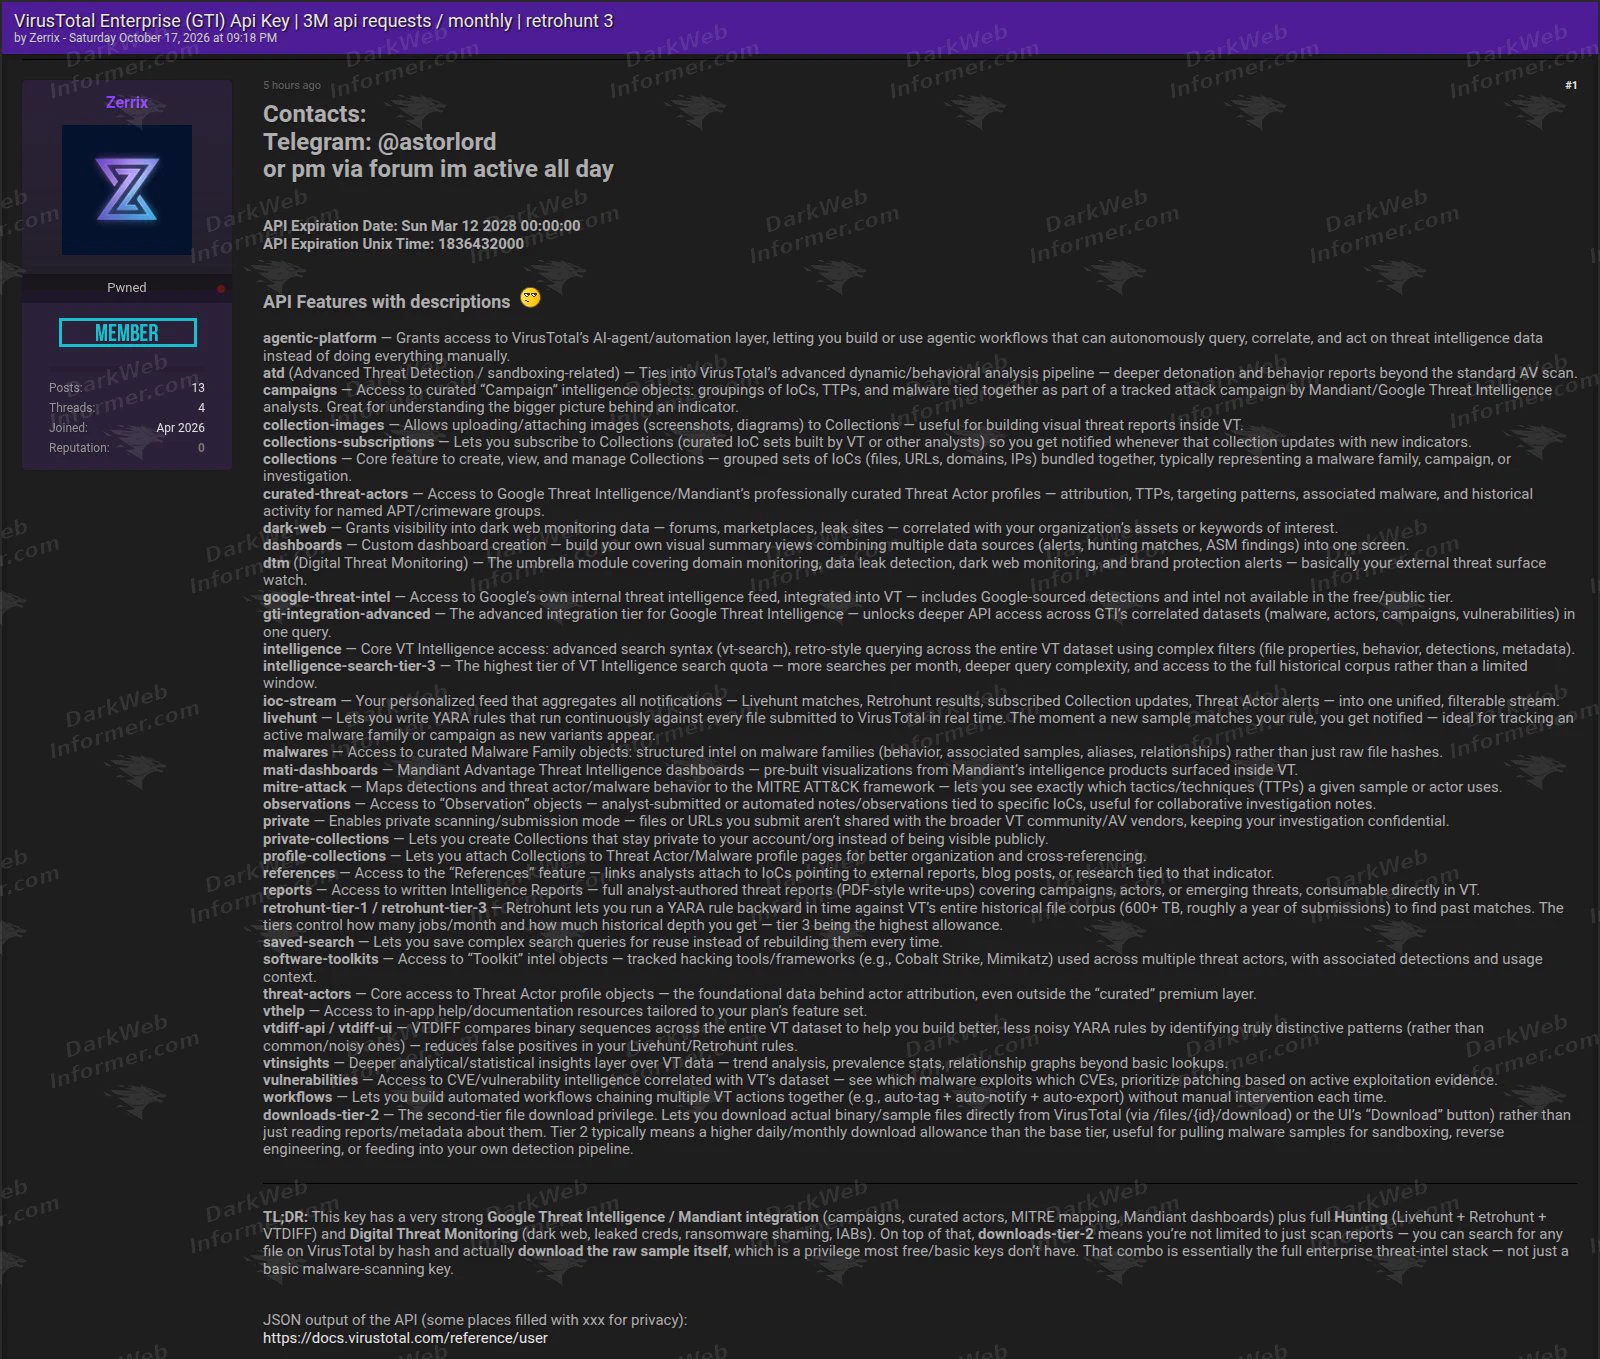
A DarkWebInformer post on an actor called "Zerrix" advertising a VirusTotal Enterprise API key for sale. The seller claims 3 million requests per month, Retrohunt Tier 3 (YARA search over historical samples), Google Threat Intelligence and Mandiant access, sample downloads and private scanning, valid until 12 March 2028. How the key was obtained is not stated, and the post says its authenticity is unverified.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security - Ethan Walkrman (@ethanwalkerman) on X
Harness2 is a framework from Google Cloud AI Research and Northwestern University in which an Editor model rewrites an agent's harness (system prompt, memory, skills, tool scripts, subagent routing, middleware) without changing model weights. It uses a Propose-Probe-Compose loop that compares execution trajectories instead of ground truth. On WorkBuddy-Bench, GLM-5 rose from 64.2 to 75.7 after one round, above Gemini 3.5 Flash at 72.4. The thread also lists risks: latency, experience poisoning, and a sandbox that is off by default.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🧠 AI  Magai (@HeyMagai) on X
Post from Magai (@HeyMagai) on Invariant Labs research showing that an approved MCP server can change its tool descriptions later without a new approval prompt, a "rug pull" like those in malicious code packages. It recommends pinning approval to tool definitions by hashing descriptions and re-prompting when the hash changes. For tools that move money, limits should stay server-side.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security- ERC-8447: Swarm AI Framework
ERC-8447 (Swarm AI Framework) is a draft Ethereum standard proposing an on-chain registry and charter model for swarms: purpose-bound agent collectives with a membership boundary, an objective with attainment rules and a declared collaboration structure. Executed terms are hashed into a frozen spec, while the charter is kept off-chain. The reference implementation has 85 Foundry tests and tender and ERC-8436 decision adapters. The thread asks reviewers about vocabulary, amendment classes and the ERC-8004 dependency.
ethereum-magicians.orgthreadAdded 19 Oct 2026, published 18 Oct 2026🧠 AI - [Draft ERC] Swarm AI Framework — registry and charter model for purpose-bound agent swarms
Ethereum Magicians discussion of a draft ERC, the Swarm AI Framework. It proposes a registry and charter model in which accounts, including autonomous agents, form, bound, run and dissolve purpose-bound swarms. A hashed on-chain SwarmSpec (roles with eligibility modules, phases, decision authorities, fallback timers) is paired with an off-chain Swarm Pack charter. Two-sided signed admission (EIP-712 / ERC-1271), challenge and substitution, and minor versus material amendments are included. Phase posture is a coordinate: executed boundary and admission, plus declared payoff, topology and coordination terms from a write-once vocabulary. This lets cooperation, competition, tenders, debate, ensembles and pipelines be expressed. It integrates with ERC-8004 agent identity and ERC-8436 decision adapters. The reference implementation is a non-upgradeable registry with five eligibility modules and a task-tender adapter. The post asks reviewers specific design questions on vocabulary, amendment classes, roster snapshots and digest kinds.
ethereum-magicians.orgthreadPublished and added 18 Oct 2026🧠 AI - Steven Daugherty (@StevenDaugherty) on X
Post warning that FastMCP had a critical flaw where a malicious MCP server could execute code on the connecting client through a crafted tool schema. Fixed in FastMCP 3.4.8 and 4.0.11, and there is no patch for the 2.x line. It matters to anyone whose agents connect to MCP servers they don't control. The post gives no CVE ID or technical root cause.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🛡️ Security  Mikko Laakkonen (@mikkolaakkonen) on X
An X thread by Mikko Laakkonen arguing that companies should encourage staff to vibe code, then provide approved hosting, identity, secrets, deployment and monitoring. It lists 200 application checks in 17 sections, from ownership and data flow through keys, authz, coding-agent isolation, appsec, SBOM and releases to recovery, runtime AI and handover. It adds 16 EU bonus checks on GDPR, NIS2, the Cyber Resilience Act (reporting from 11 Sept 2026, main duties 11 Dec 2027), the AI Act and the Data Act. It builds on Mark Ajzenstadt's production-readiness post and links a 300-check worksheet version.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🛡️ Security- Bikash | Hermes Super-Intel (@BkashJosi) on X
Post by Bikash (@BkashJosi) ranking open GitHub issues labelled type/feature for the Hermes agent framework by thumbs-up reactions. The query returned 5,349 issues and only one has more than 50 votes. The top three are Claude Agent SDK with subscription OAuth (57), remote Hermes with local tool execution (41) and Mistral provider support (32), followed by backups, configuration sync and context reduction. The full top 10 is only in the video.
x.comthreadAdded 20 Oct 2026, published 17 Oct 2026🧠 AI  🚨 AI News | TestingCatalog (@testingcatalog) on X
A TestingCatalog X post with two Daily AI Briefs (Oct 17 and the start of Oct 16), grouped by vendor. Oct 17 items include GPT-6 Astra Pro upgrades in ChatGPT, Codex context reuse and caching, Gemini 4 Argon in AI Studio Build, the open-weight MIT-licensed DeepSeek-V4.1-Flash-1017, Claude Code Review going GA, Perplexity's open Decider v1.2 models (27B and 4B), NVIDIA's 4B looped Nemotron Labs Dory 1.0, Reflection's Apache-2.0 Beam, Cursor cloud-agent canvases and Tencent's Hy Memory 2.0. Oct 16 begins with Meta's open-weight Muse Spark Open, an 816B-total, 42B-active MoE with a 1M-token context. It gives a quick snapshot of the week's open-weight and coding-agent releases.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🧠 AI- Master the captain (@mollicksoif9) on X
A social post reporting that Reflection AI released the full weights of Beam, a 501B-parameter mixture-of-experts agentic coding model (23B active, 1M-token context), on Hugging Face under Apache 2.0. It claims RL training that penalizes wasted tokens gives roughly 3-4x less inference compute than GLM-5.2, and 80.9 on SWE-bench Verified. Launch support is listed for AWS SageMaker, vLLM and SGLang. The post notes the token-efficiency claims still need independent confirmation and that self-hosting needs about 500GB of GPU memory at 8-bit.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🧠 AI - CyrilXBT (@cyrilXBT) on X
REA (github.com/morluto/rea) is an open-source tool that lets an agent such as Claude Code run reverse-engineering tools (Ghidra, IDA, JADX) on a local machine and return findings with evidence. Targets named are desktop apps, compiled programs and games, Android apps, website network traffic, and firmware or binaries. The post claims a DX Ball sound function was rebuilt to byte-identical code. Setup is `npx rea-agents setup`, and the author says to use it only on software you own or may analyze.
x.comthreadAdded 19 Oct 2026, published 17 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
Post summarizing independent researcher Sammy Azdoufal's report on EnergizeLab's Eilik companion robots, which are marketed mostly to kids. Per the report, any registered user could read other families' chat transcripts through the vendor back office. An unauthenticated endpoint also lets anyone swap the robot's AI model, voice and personality (CVE-2026-105038, CVSS 9.8, PoC listed by the CNA). At the Oct 13 retest, 32 of 40 remotely testable findings were still open. The post notes that The Verge demonstrated the issue on its reporter's own toy, that vendor remediation is unverified, and that broader malicious compromise is unproven.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🛡️ Security  Nicholas Martin (@ndgmlondon) on X
An X post advises auditing every MCP write tool against the database role it actually runs under. A shared service key lets prompt injection trigger unapproved writes, so each agent session should get a read-only role, with a test that writes are denied. Replies note that MCP servers often inherit ambient host credentials or can escalate through a second connection pool, and suggest also testing that another tenant's rows are unreadable with the same role.
x.comthreadAdded 18 Oct 2026, published 16 Oct 2026🛡️ Security- Peter Dedene (@dedene) on X
A X thread benchmarking Qwen3.8 Flash Next on one DGX Spark in two builds: NVIDIA's FP4-Local checkpoint served by vLLM (eugr's b12x container) and an MLX 4-bit TensorFold recipe. The NVIDIA build scores higher on the author's agentic benchmark (81.2 vs 75.0), BFCL tool calling (82.4 vs 71.8 single-turn, 54.5 vs 43.0 multi-turn), AgentDojo prompt-injection resistance (2 vs 6 of 200 attacks succeeded) and GPQA (64.6 vs 59.1). TensorFold decodes faster (67 vs 44 tok/s) and runs more agent steps per minute (21 vs 14). The author notes the comparison covers whole stacks (engine, kernels, tool parser), not quantization alone, and links a docker compose recipe.
x.comthreadAdded 17 Oct 2026, published 16 Oct 2026🧠 AI - Trail of Bits (@trailofbits) on X
Trail of Bits post announcing research that tested 25 package managers against a simulated malicious repository serving swapped code for the same package and version. Without a lockfile only Go and vcpkg verified every download; with a lockfile fewer than half did. This undercuts the assumption that lockfiles make dependencies immutable and shows hash/integrity verification gaps across ecosystems.
x.comthreadAdded 18 Oct 2026, published 16 Oct 2026🛡️ Security - !Manan (@0xManan) on X
Social post describing CVE-2026-97229, a CVSS 10 unauthenticated RCE in GitLab CE/EE. A crafted .gitlab-ci.yml with a UTF-8 path passes validation under US-ASCII, then is recompiled by the Onigmo regex engine, where an integer wraps at INT_MAX. That gives attacker-controlled VM ops and system() execution as the git user. The chain is to push a payload to a public project, then call unauthenticated GET /api/v4/projects/:id/ci/lint. It links a Rapid7 PoC and writeup and lists fixed self-managed versions 19.2.8, 19.3.5 and 19.4.2. GitLab.com is already patched.
x.comthreadAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security - P.K. Sharma (@_pksharma) on X
Thread distinguishing two Langflow advisories on MCP Stdio command execution. CVE-2026-105740 (GHSA-7w94-79vh-5mr2) affects 1.8.3 and is fixed in 1.9.0, an authenticated non-admin path. CVE-2026-105697 (GHSA-w794-rj3p-xv45) covers 1.1.2 up to but excluding 1.10.3, with fixes in lfx and langflow-base too. The later fix validates the API, flow and pre-spawn boundaries and removes the shell wrapper, and the thread warns that LANGFLOW_AUTO_LOGIN=true can expose a token without credentials. It cites one sensor's telemetry (1,628 attempts from 28 IPs) with caveats, and gives a defensive checklist: verify patched packages, review stored MCP configs and imported flows, and hunt for unexpected child processes.
x.comthreadAdded 17 Oct 2026, published 15 Oct 2026🛡️ Security
















Showing 90 of 167
Show more