Adobe, Veeam, Juniper Networks Patch Critical Vulnerabilities
SecurityWeek roundup of patches from Adobe, Veeam and Juniper Networks covering over three dozen vulnerabilities. Adobe fixed 12 flaws (eight critical in Campaign Classic), Veeam fixed nine (including a cross-tenant RCE in Backup for Microsoft 365), and Juniper fixed 18 in Session Smart Router and Conductor. None were reported exploited. Juniper said CVE-2026-109618 (PHP2Shell) affects Junos OS but is not exploitable there.
 securityweek.comarticlePublished and added 29 Oct 2026🛡️ Security
- CISA Publishes Significant Updates to ScubaGear and ScubaGoggles
ScubaGear v2.0 and ScubaGoggles v1.1.0 are CISA's updated SCuBA assessment tools for Microsoft 365 and Google Workspace secure configuration baselines. ScubaGear now uses direct REST API calls, adds Power BI coverage, a consolidated Security Suite baseline and app severity scoring. ScubaGoggles adds a GUI, Policy API integration and Gemini controls. The release supports BOD 25-01 compliance.
 cisa.govarticleAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security
- Unboxing Phishing Kits: Huntress Examines 3 Real Kits
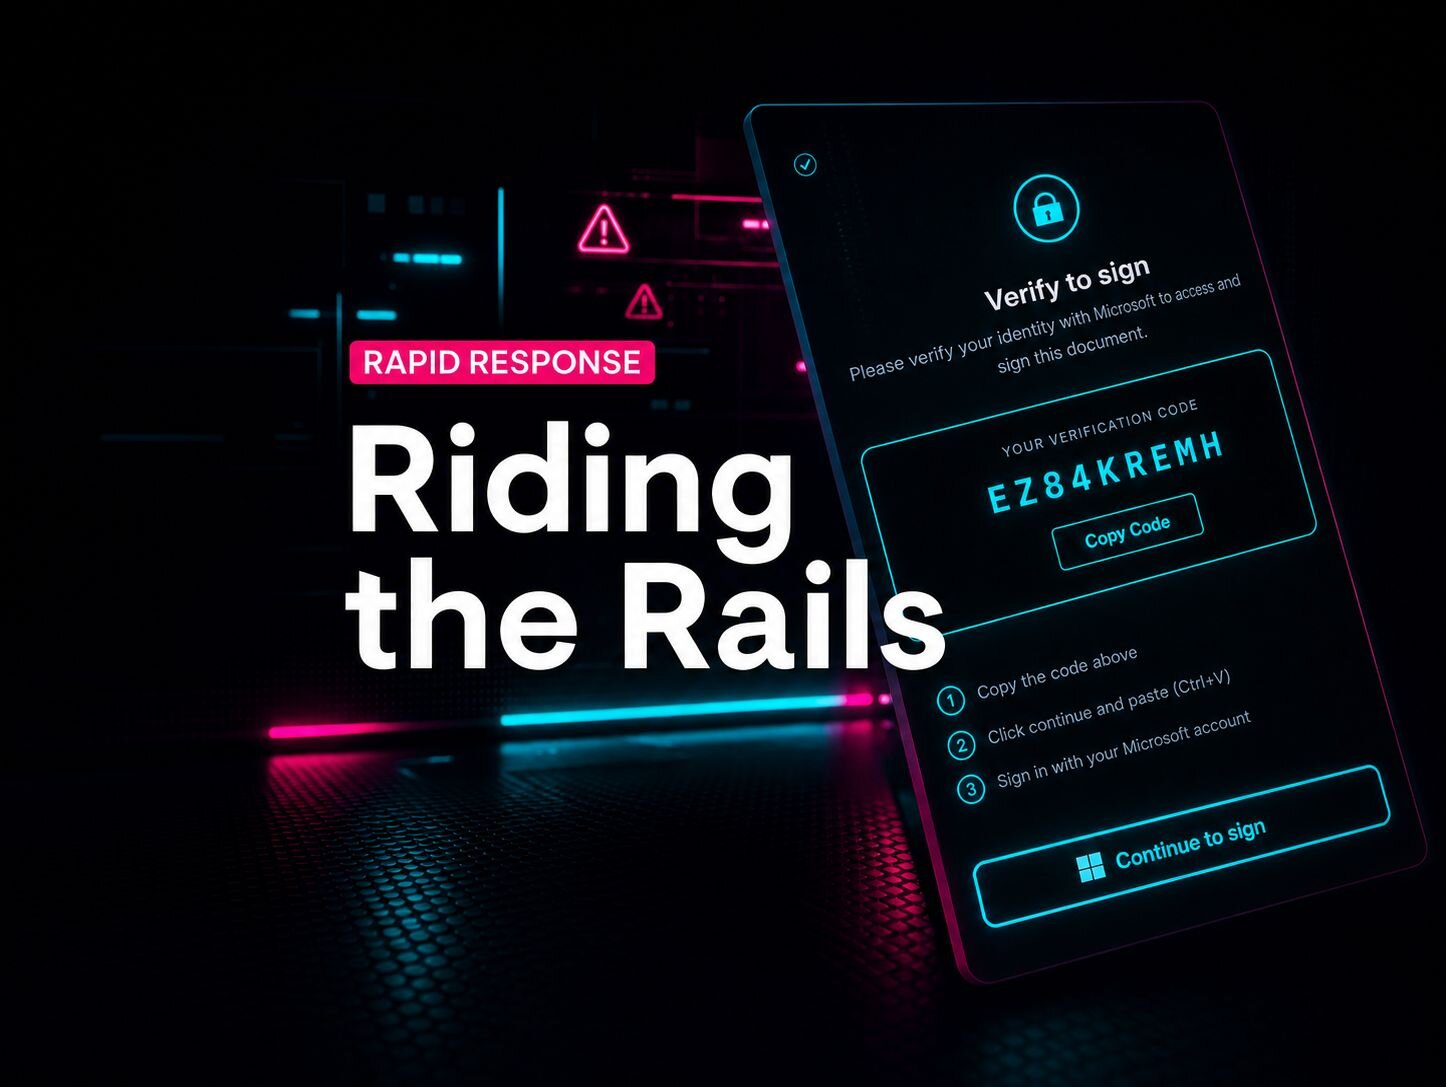
Recap of a Huntress Tradecraft Tuesday session (October 2026) on phishing kits that target Microsoft 365 tokens, including EvilTokens (a device-code phishing campaign abusing Railway) and the Kali365 control panel. It explains device-code phishing, adversary-in-the-middle and token replay. It lists detections (unfamiliar cloud sign-ins, device-code auth, new devices) and response steps (revoke refresh tokens, remove rogue devices, block device-code flow).
 huntress.comarticlePublished and added 22 Oct 2026🛡️ Security
- M365 Token Spray and Replay Campaign Compromises Business Email Accounts
Huntress analysis of a July to September 2026 token replay ("token spraying") campaign: 497 successful Microsoft 365 sign-ins across 79 organizations, replayed from six addresses in 193.26.115.0/24 (1337 Services GmbH). Tokens came from AiTM relays, device-code phishing and social engineering. It covers four phases, rogue Entra devices, MFA method swaps, hidden inbox rules, hunting queries and Conditional Access guidance.
huntress.comwriteupPublished and added 22 Oct 2026🛡️ Security  ConnectWise Suspends Cloud Services in Response to Cyberattack
ConnectWise suspended its Cloud Backup (formerly SkyKick), SaaS Security and Cloud Management services in October 2026 after a compromised application credential was used to access customers' Microsoft 365 tenants. Huntress saw the Cloud Backup identity sign in to 162 tenants on 15 to 16 October and attacker IP 144.172.64[.]128 try nearly 1,000 Entra tenants, with over 300 successful sign-ins. In one tenant, the Cloud Management Teams app added itself to Global Administrator and added client secrets to other apps. No restoration timeline has been given.
securityweek.comarticlePublished and added 19 Oct 2026🛡️ Security The hidden network: Inside the phishing infrastructure ecosystem powering global cybercrime
Microsoft Threat Intelligence maps a Chinese-language cybercrime ecosystem: the YAM Store (Storm-3119), an initial access broker that hijacks Microsoft 365/Azure Education tenants and resells accounts, licenses and SharePoint/OneDrive storage, and the Storm-2990 phishing kits (CoGUI, Haozi, Iron Man System) sold via Telegram. It details the five-stage broker pipeline (app-only client-secret abuse, PnP Management Shell service principal, Graph permissions, Cloudflare DNS management), kit evasion features (geofencing, fake CAPTCHA, WebSocket/Telegram live interaction, 2,335+ templates), downstream device-code phishing and card fraud, and lists mitigations such as passkeys, phishing-resistant MFA and Conditional Access. Microsoft's DCU facilitated a disruption with law enforcement; kits sent over one billion messages since January 2026.
 microsoft.comarticlePublished and added 14 Oct 2026🛡️ Security
 Microsoft Disrupts Chinese-Language Phishing Market Behind 1B+ Messages
Microsoft and Health-ISAC seized domains tied to YAM Store (Storm-3119), an access broker that hijacks Microsoft 365 and Azure for Education tenants, and to the Storm-2990 phishing kits CoGUI, Haozi and Iron Man, under a Southern District of Florida order. The services sent over 1B malicious messages since January 2026 to 75,000+ organizations in 150+ countries; Microsoft disabled 20,000+ accounts and is blocking 100,000+ domains. Iron Man offers 2,335+ templates and real-time OTP capture, and Resecurity found it needs regular contact with a vendor licensing server, a dependency defenders can exploit.
securityweek.comarticlePublished and added 14 Oct 2026🛡️ Security- Ned Peterson (@NedPeterson99) on X
A post summarizing a joint FBI and six-country advisory on actors tied to Integrity Technology Group (the sanctioned Chinese firm linked to Flax Typhoon and the Raptor Train botnet). They password-sprayed Microsoft 365 and Exchange accounts over EWS, OWA, ActiveSync and PowerShell with EBurst. They then drained mailboxes with a PHP bot over Exchange Web Services and an office-cli utility using stored client ID, tenant ID and secret values, and exposed the stolen email to third parties through a web app, in some cases restricted to Xiamen IP addresses. Victims were in government, law enforcement, healthcare and religious organizations across Southeast Asia, Africa and North America, with activity since at least January 2021. Defensive takeaways: enforce MFA on every legacy path, retire basic auth and EWS, audit OAuth apps and service principals with mail-read rights, and alert on bulk mailbox pulls.
 x.comthreadAdded 11 Oct 2026, published 9 Oct 2026🛡️ Security
 Google Wants Gemini to Be Your Next Coworker—Complete With Its Own Email Address
Decrypt reports on Google Cloud's newly announced Gemini Agent, a long-running AI agent that operates across Gmail, Docs, Sheets, Slides, Drive, Chat, Calendar, Microsoft 365 and Slack, and can run for hours or days on a single goal. The feature allows managers to spin up coworker agents with their own Workspace email address, calendar, Drive storage and directory listing, each given a cryptographically attested identity and a separate audit trail; agents connect to Salesforce, ServiceNow, Jira, Snowflake, BigQuery and any Model Context Protocol server, and are orchestrated across both Gemini and Anthropic's Claude models depending on cost and quality fit. Google pairs the launch with safety infrastructure, an Agent Sandbox, an AI network firewall called Agent Gateway, and real-time token-spend caps, citing a prior Claude Cowork VM-escape finding by Accomplish AI as the kind of containment failure it is designed to prevent.
 decrypt.coarticlePublished and added 8 Oct 2026🧠 AI
 Detecting and countering misuse of AI: September 2026
Anthropic Threat Intelligence report covering misuse of Claude disrupted between December 2025 and August 2026 across seven harm areas. The visible cyber section details a Russian espionage actor (GTG-20006, linked to Midnight Blizzard) that used AI agents to rebuild malware flagged by security products, ran DNS hijacking via hotel WiFi vendors, and used device-code phishing against Microsoft 365. It also covers ShinyHunters-affiliated smash-and-grab extortion (GTG-50014), a Chinese-speaking exploit-foundry group running agent swarms for appliance zero-day research (GTG-10007), and fraudulent AI resellers that harvest API keys (GTG-50021). IOCs are included. Only the first 40k of ~220k characters were seen.
 anthropic.comarticleAdded 18 Sep 2026🛡️ Security
 Passkey-themed social engineering leads to identity and cloud compromise
Microsoft Security Research details an active campaign (since May 2026) where attackers use voice-phishing and SMS lures impersonating IT helpdesk passkey/SSO enrollment requests to drive victims into AiTM or device-code phishing flows, compromising Microsoft 365 identities. Post-compromise, actors register attacker-controlled MFA methods (e.g., software OTP tokens) for persistence, conduct systematic Microsoft Graph reconnaissance across users, groups, roles, and SharePoint/OneDrive/Exchange, then exfiltrate data at a measured pace using automated Node.js/python-httpx tooling while evading detection through IP rotation and anonymous proxies. The post includes real audit-log JSON examples, multiple KQL hunting queries for GraphAPIAuditEvents/CloudAppEvents, full MITRE ATT&CK mapping, and attributes the initial-access tradecraft to Storm-3121 and Storm-3032, which feed into ShinyHunters/Falcon and Helix extortion operations.
microsoft.comwriteupAdded 3 Oct 2026, published 9 Sep 2026🛡️ Security- Inside Knight Office, a New M365 AiTM Phishing Kit
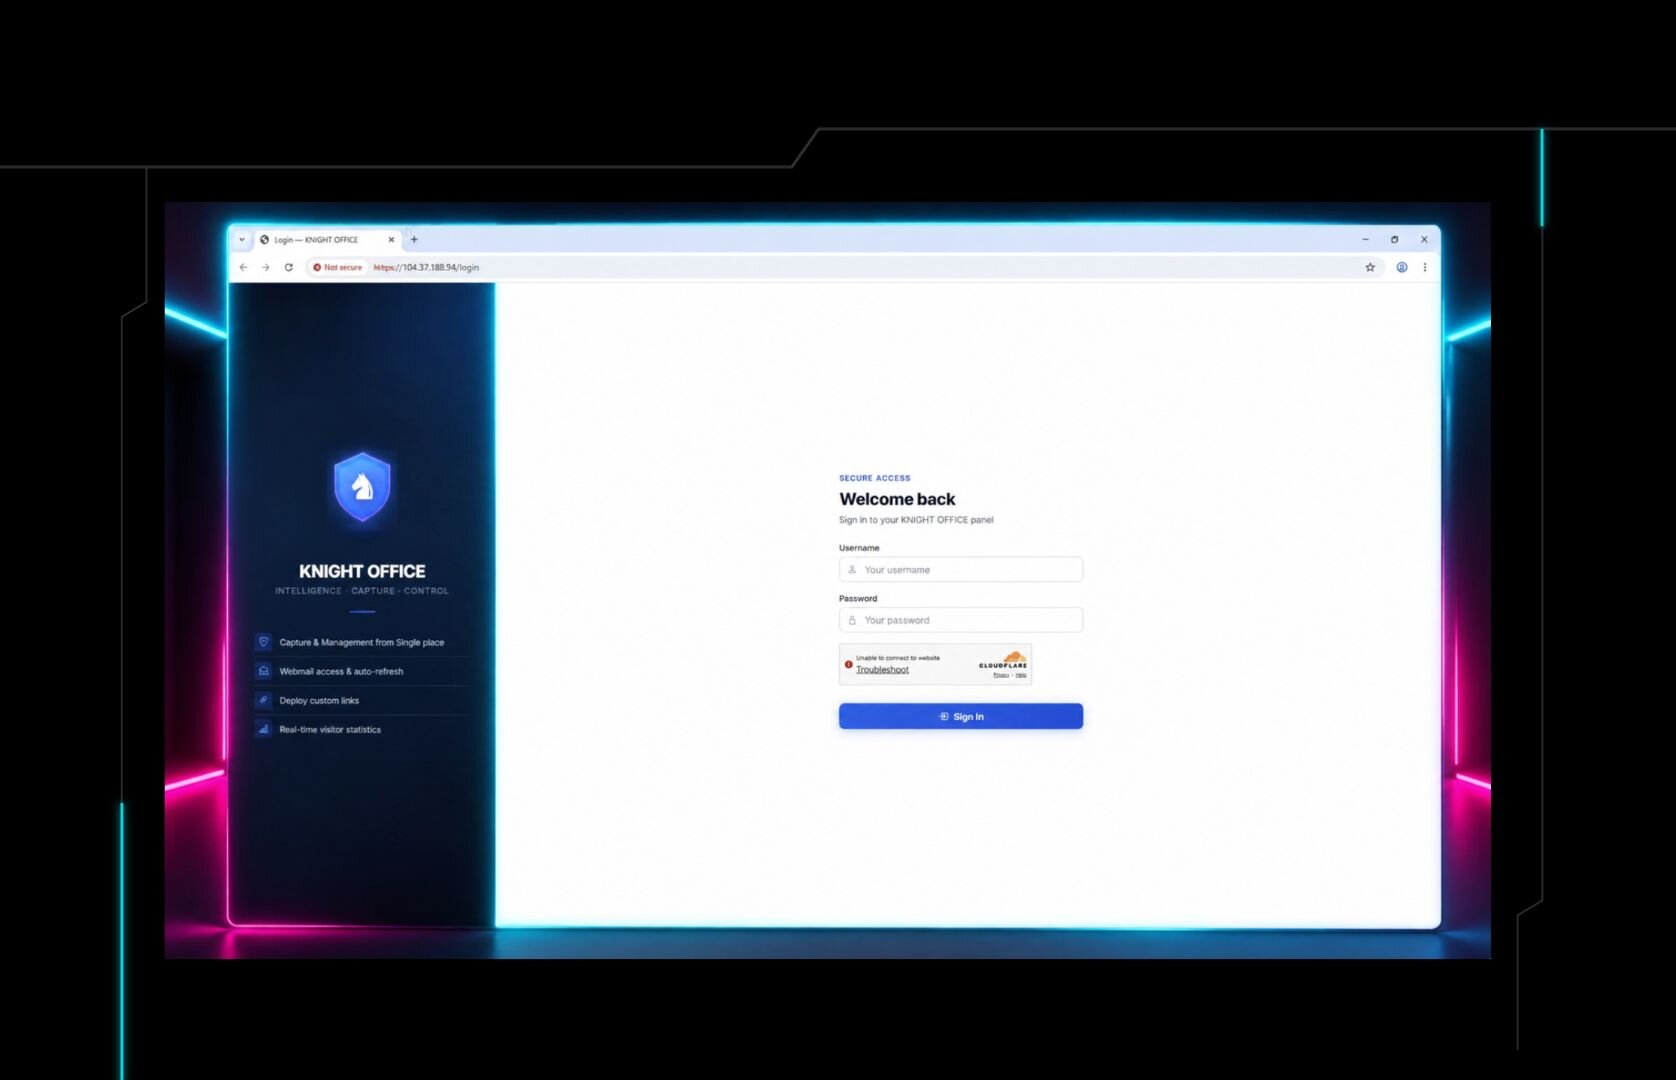
Huntress researchers uncovered the operator console for "Knight Office," a Flask-based adversary-in-the-middle (AiTM) phishing kit used to steal Microsoft 365 session tokens via a DocuSign-themed, self-spoofed lure that routes victims through Monday.com redirects and a compromised Joomla site to a fake Microsoft device-code authentication page. After capturing tokens, the attacker registered a rogue device in Microsoft Entra ID and bound a Windows Hello for Business key credential to the compromised account to maintain persistent, MFA-bypassing access even after token revocation. The writeup details IOCs (IPs, .vu domains, User-Agent strings), links the campaign to hundreds of reported phishing emails since April, and gives defenders concrete hunting/response steps around callback-proxy sign-ins and newly registered WHfB credentials.
huntress.comwriteupAdded 8 Sep 2026, published 2 Sep 2026🛡️ Security - Insights into Suspected DPRK Workers
Huntress details investigations into five suspected DPRK (FAMOUS CHOLLIMA) remote workers who infiltrated partner organizations in IT, sales/marketing, and healthcare roles in 2026. The writeup covers detection methodology using Microsoft 365 Unified Audit Logs, Huntress ITDR, and analysis of infrastructure (Astrill VPN, IPRoyal Proxy, WorkTitans B.V. bulletproof hosting), plus forensic evidence of fraudulent identity documents (fake Chinese passports/ID cards with matching forged details) used during onboarding.
huntress.comwriteupAdded 3 Sep 2026, published 26 Aug 2026🛡️ Security - A Detection Engineer's Guide for Delegating Work to AI
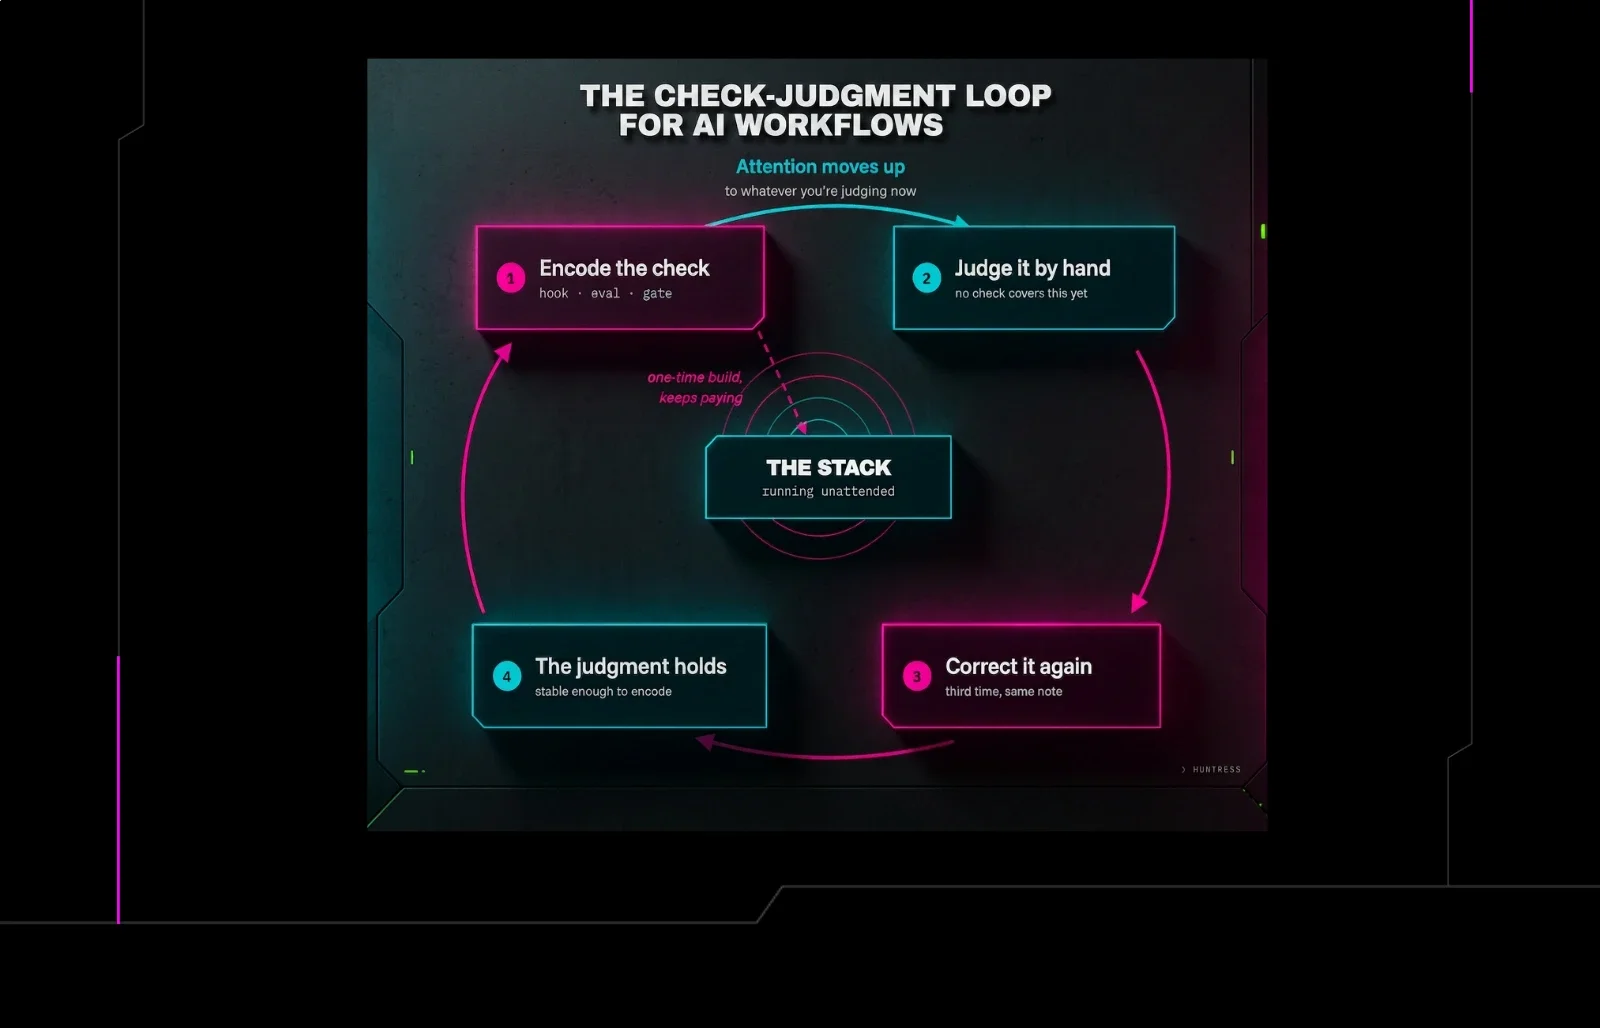
A Huntress detection engineer describes using an LLM to analyze a Microsoft 365 account-takeover case: the model flagged an app identifier as malicious, but it turned out to be the legitimate Outlook desktop client (present in 17%+ of customer orgs) — a scoping error caused by comparing against the wrong denominator. Rescoping the same query correctly surfaced the actual malicious tooling (an identifier seen in only three orgs, rewriting inbox rules), which shipped as a live detection rule with true positives and no false positives so far. The piece generalizes this into a framework for delegating detection-engineering work to AI: only hand over tasks you can cheaply and reliably verify, and invest in building fast, repeatable checks (coverage checks, alert-volume checks, known-good/known-bad tests) rather than trusting raw LLM output.
huntress.comarticleAdded 3 Sep 2026, published 19 Aug 2026🛡️ Security  UNC6671 Rebrands: Multi-Brand Vishing Extortion Targets Financial Services and Enterprise Cloud Environments
UNC6671 is a vishing and extortion cluster that GTIG links to the BlackFile, Redact, Pink, Helix and Falcon brands through shared passkey-themed AiTM phishing domains and identical templates. Callers pose as IT helpdesk on personal phones, harvest credentials and MFA tokens, then script data theft from Microsoft 365 and Okta. The post covers targeting shifts to financial and legal firms, 141.65 BTC in ransom payments, hardening guidance and Okta/M365 detections.
 cloud.google.comarticleAdded 29 Oct 2026, published 6 Aug 2026🛡️ Security
- Device Code Phishing Keeps Evolving. Here’s What to Watch For
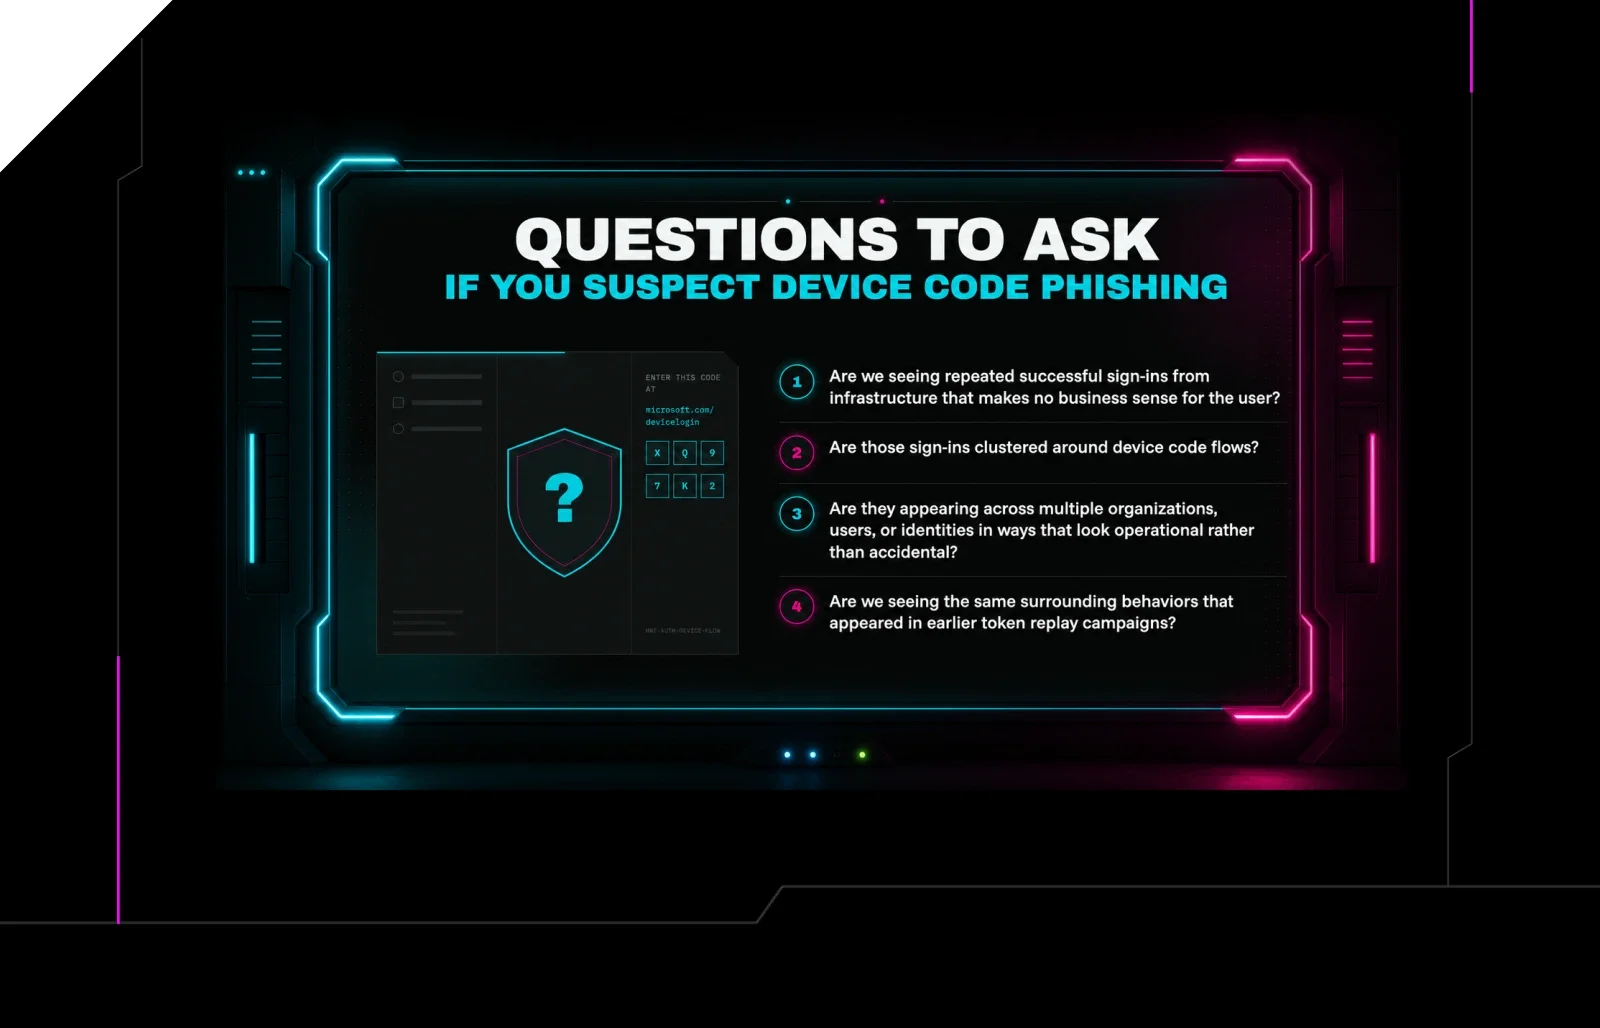
Huntress details a second 2026 wave of device code phishing against Microsoft 365, this time abusing VPS reseller BL Networks (BitLaunch/BLNWX, AS399629) after an earlier wave tied to Railway and the EvilTokens phishing-as-a-service kit. Huntress observed 533 malicious events and 113 successful logins from a single BL Networks IP in April, spreading across multiple IPs and subnets by May, with 26 critical incidents across 23 identities logged in July, and argues defenders must stop trusting infrastructure reputation and instead hunt for anomalous device-code sign-in clusters and revoke tokens quickly. It ties the activity to the broader legitimate-cloud-plus-legitimate-Microsoft-auth-page attack pattern also seen with Railway, EvilTokens, and Kali365.
huntress.comwriteupAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security - Conditional Access Misconfigurations Exposed 55 Orgs with MFA On
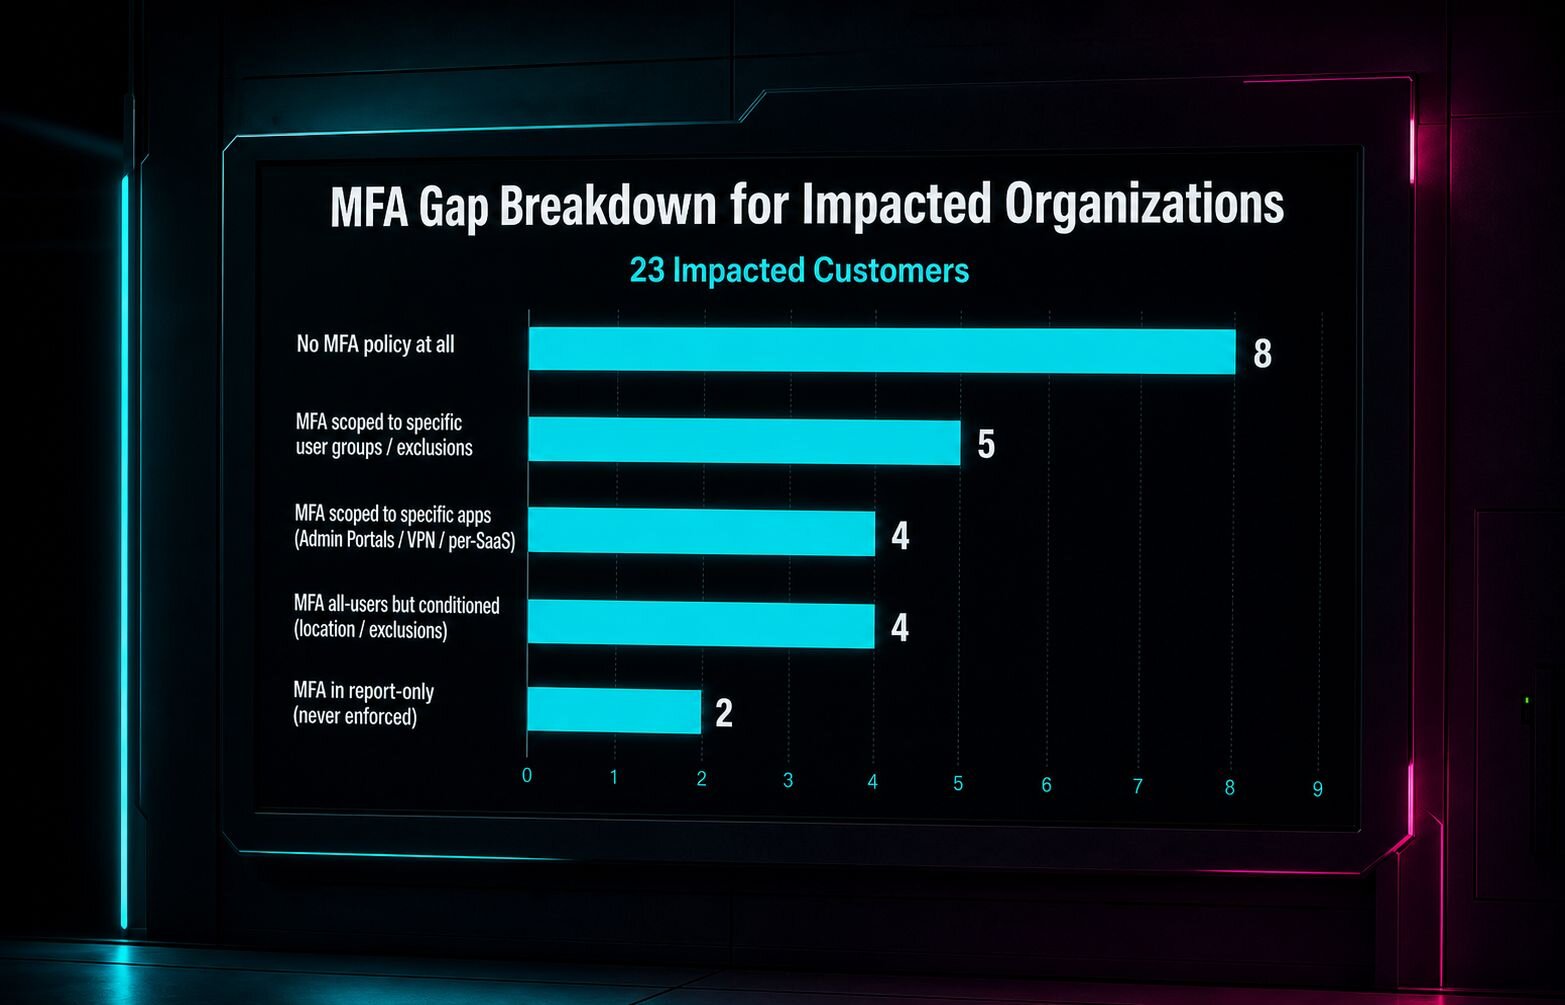
Huntress details two 2026 campaigns that bypassed Microsoft 365 MFA despite Conditional Access policies being in place: device code phishing abusing Railway.com's clean IP infrastructure, attributed to the EvilTokens phishing-as-a-service platform, hitting 344 orgs, and a ROPC-based credential replay attack from LSHIY LLC infrastructure with 81 million login attempts and 78 compromised accounts, 55 of which had active MFA policies that didn't actually cover Azure CLI or legacy auth. It breaks down how narrow Conditional Access policy scoping, missing All Cloud Apps coverage, excluded user groups, report-only mode, mislabeled trusted locations, let attackers through, and recommends blocking device code flow and legacy auth via Conditional Access as the fix.
huntress.comarticleAdded 3 Sep 2026, published 9 Jul 2026🛡️ Security  Copirate 365 at DEF CON: Plundering in the Depths of Microsoft Copilot (CVE-2026-24299) · Embrace The Red
Johann Rehberger's writeup of his DEF CON Singapore talk detailing a multi-stage exploit chain against Microsoft 365 Copilot and Consumer Copilot (CVE-2026-24299): indirect prompt injection triggers Copilot's HTML preview feature, CSS background-image/font-face rules bypass img-src CSP and exfiltrate data over font-src, and the attack is made zero-click by instructing Copilot to auto-open the preview. It further chains this with abuse of Copilot's record_memory / durable-facts long-term memory tools (which have no audit logging) to plant persistent "SpAIware"-style instructions that silently exfiltrate any password or secret the user later types, plus Delayed Tool Invocation as a reliability trick and edge_navigate_to abuse in Edge's Copilot to leak stored memories. Includes full disclosure timeline (Oct 2025 report to Dec 2025/Mar 2026 fixes) and broader lessons on CSP not being a reliable AI security boundary and the "lethal trifecta."
 embracethered.comwriteupAdded 6 Jul 2026🛡️ Security
- No (Bad) CAP: Inside an Ongoing LSHIY Password Spray Attack
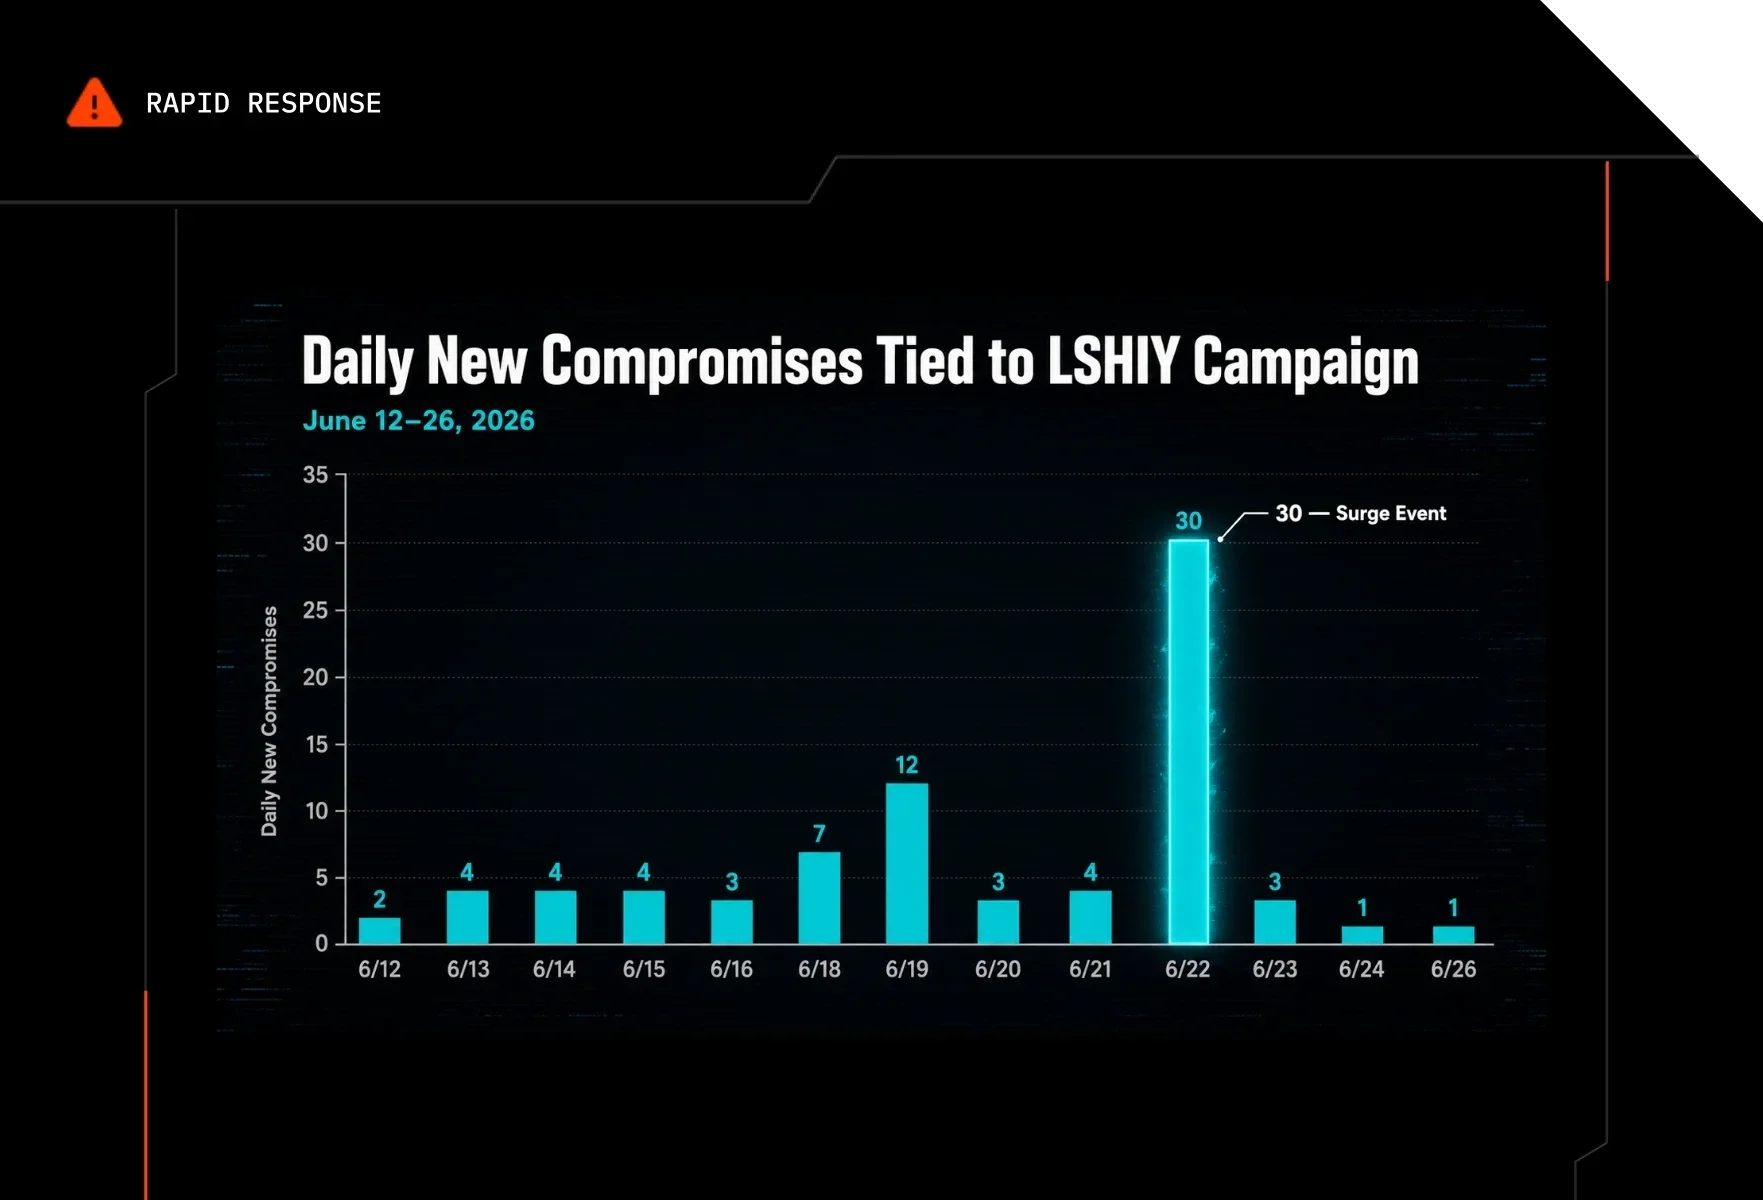
Huntress tracked a large, ongoing password spray campaign against Microsoft 365/Azure CLI using the deprecated OAuth ROPC (Resource Owner Password Credentials) flow, which sends passwords directly to the /token endpoint and bypasses MFA prompts enforced via Conditional Access Policies. Between June 12-26, over 81 million login attempts from LSHIY LLC's IPv6 range (AS32167) compromised 78 accounts across 64 organizations, many of which had MFA enabled but scoped incorrectly (app-specific, group-specific, trusted-location exceptions, or report-only mode). After LSHIY terminated the abusive BYOIP customer, attackers pivoted to FranTech (AS53667) and then 3xK Tech GmbH (AS200373), rotating through ~12,800 IPv4 addresses at low per-IP volume to evade detection while sustaining ~1.5 million login attempts/day.
huntress.comwriteupAdded 3 Sep 2026, published 30 Jun 2026🛡️ Security - The Hacker's 2026 Playbook: Dark Web Tactics Targeting You
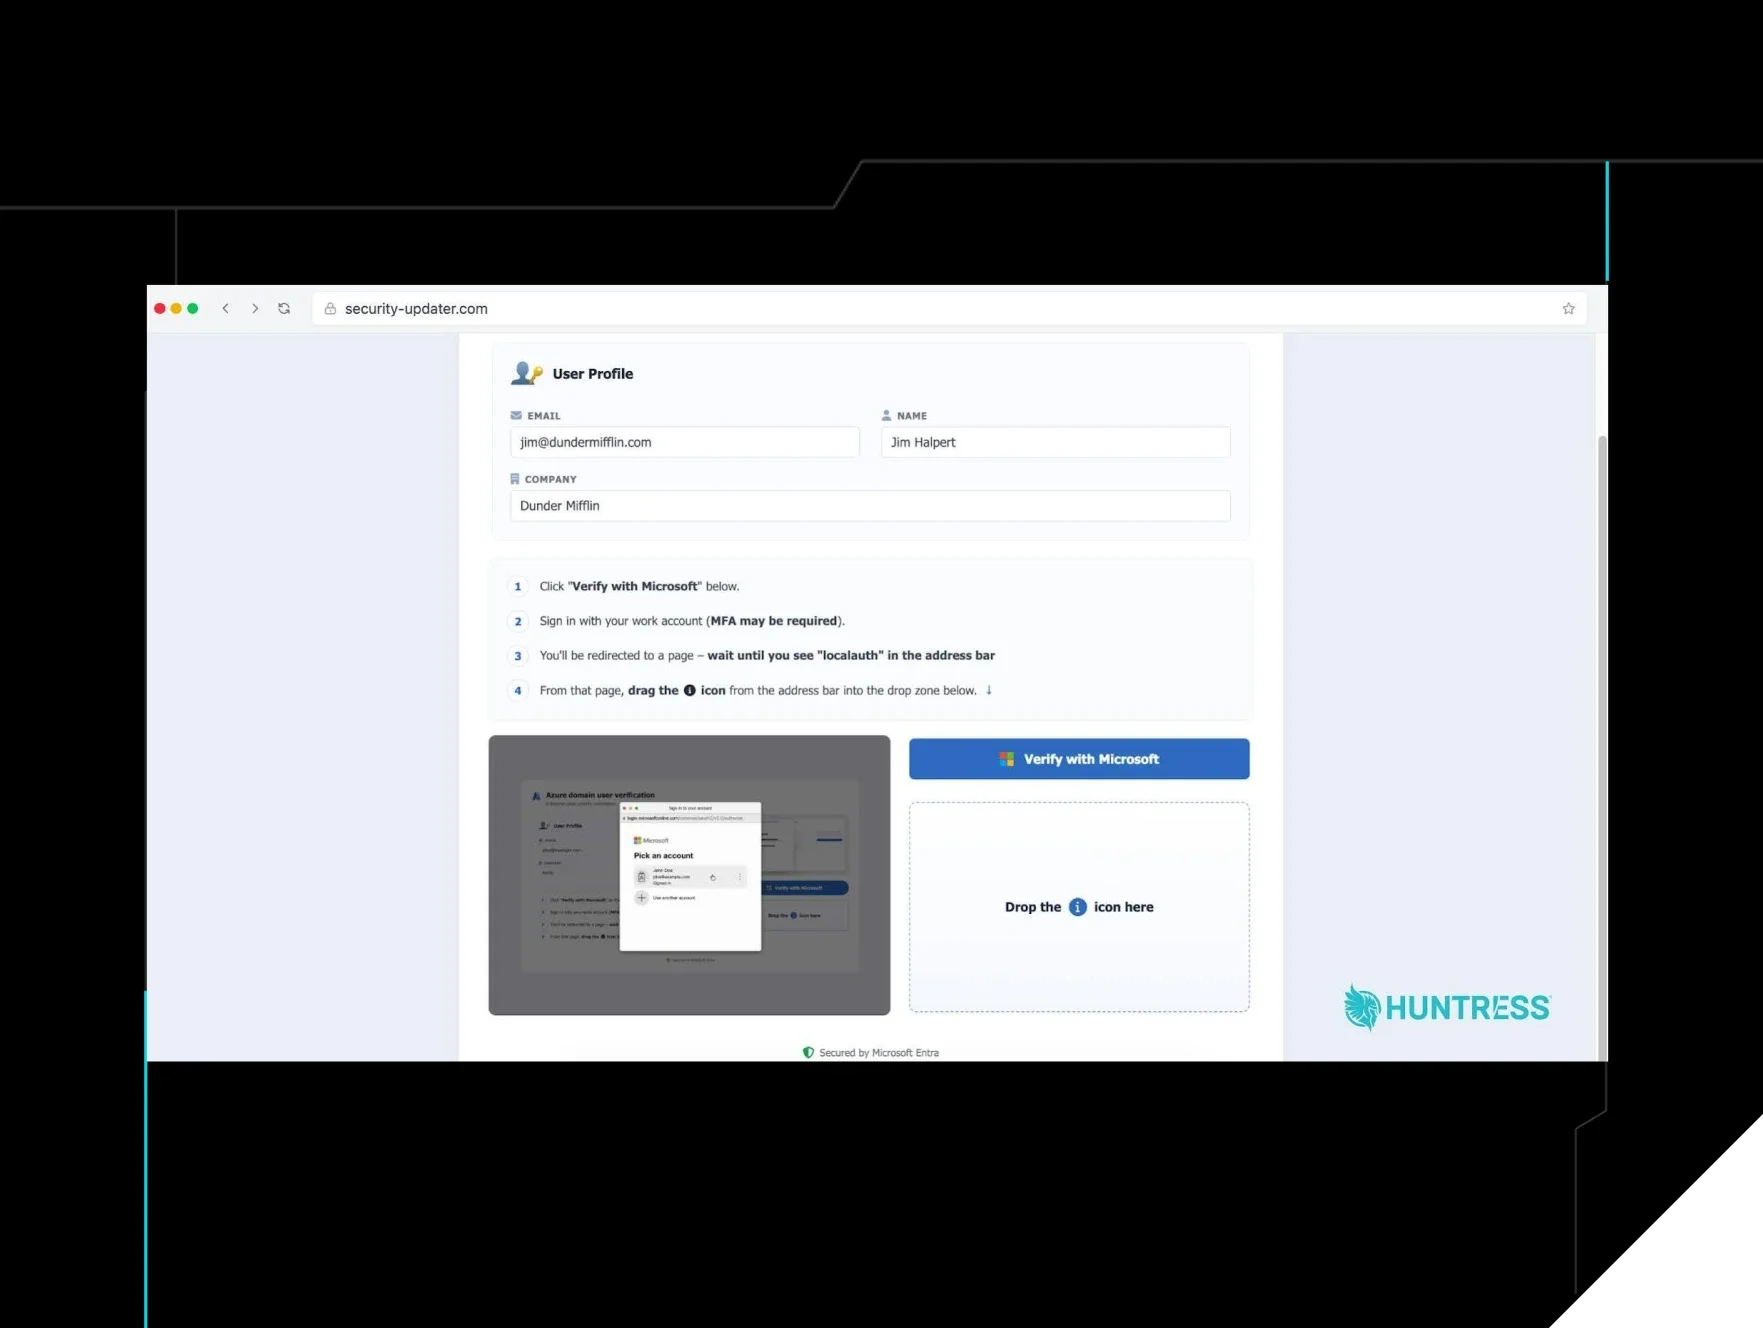
Huntress details ConsentFix, an evolution of ClickFix that abuses Microsoft 365 OAuth sign-in flows: victims are phished via password-protected Dropbox or DocSend lures, shown a fake Microsoft sign-in page, and tricked into dragging a localhost callback link into their browser, which exfiltrates OAuth tokens and hijacks the session without needing a password or triggering MFA. A cybercrime forum post published the full technique with working code and infrastructure such as Cloudflare Pages, workers.dev, and Pipedream webhooks, and showed attackers using LinkedIn, ZoomInfo, and Hunter.io to profile victims before sending lures.
huntress.comarticleAdded 3 Sep 2026, published 29 Jun 2026🛡️ Security  SearchLeak: How We Turned M365 Copilot Into a One-Click Data Exfiltration Weapon
Varonis Threat Labs details SearchLeak, a three-stage exploit chain (CVE-2026-42824, critical) that abuses Microsoft 365 Copilot Enterprise Search: a Parameter-to-Prompt (P2P) injection via the search URL's `q` parameter turns a clicked link into an AI instruction, an HTML-rendering race condition lets an injected `<img>` tag fire before Copilot's `<code>`-block sanitizer applies, and Bing's "Search by Image" endpoint (allowlisted in the CSP) performs a server-side fetch that exfiltrates the stolen data to an attacker's server. A single click on a trusted microsoft.com link lets an attacker silently exfiltrate emails, security codes, calendar data, and SharePoint/OneDrive content with the victim's full Graph permissions, no plugins or extra permissions required. Microsoft has patched the issue; the post is a follow-up to Varonis' earlier "Reprompt" finding in Copilot Personal.
 varonis.comwriteupAdded 16 Jun 2026, published 15 Jun 2026🛡️ Security
 New attack turned Microsoft 365 Copilot into 1-click data theft tool
BleepingComputer covers Varonis's SearchLeak research, a three-stage attack chain (CVE-2026-42824, now patched) affecting Microsoft 365 Copilot Enterprise Search. Attackers craft a URL with a malicious 'q' parameter to prompt-inject Copilot into searching a victim's mailbox/OneDrive/SharePoint, exploit an HTML-rendering race condition to slip an unsanitized img tag past output neutralization, then abuse an SSRF in Bing's "Search by Image" feature to bypass CSP and exfiltrate the stolen data (emails, passwords, meeting details) to an attacker-controlled server via a single click, no user typing required.
 bleepingcomputer.comarticleAdded 26 Sep 2026, published 15 Jun 2026🛡️ Security
- From Cookies to Keys: The Threat of Session Hijacking
Huntress breaks down how session hijacking has overtaken password theft, with infostealer malware (e.g. RedLine) harvesting browser cookies/tokens for Google Workspace, Microsoft 365, Slack, GitHub, and AWS. It details the dark-web economy for these tokens (pricing from $5 logs up to $1,000+ "Developer Access Bundles" resold by initial access brokers), the replay tooling used (OpenBullet, StealyBot), and defensive measures like short-lived sessions, Secure/HttpOnly cookies, and canary credentials.
huntress.comarticleAdded 3 Sep 2026, published 26 May 2026🛡️ Security  Prompt Injection Attack Compendium (2026 Edition)
A comprehensive compendium mapping the prompt injection attack surface: direct vs. indirect vectors, the HouYi three-part payload structure (from Liu et al.'s study finding 31 of 36 tested LLM apps, including Notion, vulnerable), and web-delivery techniques like zero font-size spans, off-screen CSS and SVG comment injection documented in Palo Alto Unit 42's analysis of 12 in-the-wild attacks. It contrasts CVE-2024-5184 (direct injection in EmailGPT via its own API) with CVE-2025-32711 "EchoLeak" (CVSS 9.3, zero-click indirect injection in Microsoft 365 Copilot), then walks through detection layers (input/output classifiers, canary tokens, tool-call anomaly detection) and ranked defenses (capability restriction, structured parsing, spotlighting, human-in-the-loop).
 aisec.blogarticleAdded 16 Sep 2026, published 11 May 2026🛡️ Security
- OpenClaw, Rogue Agents, and Application Hygiene
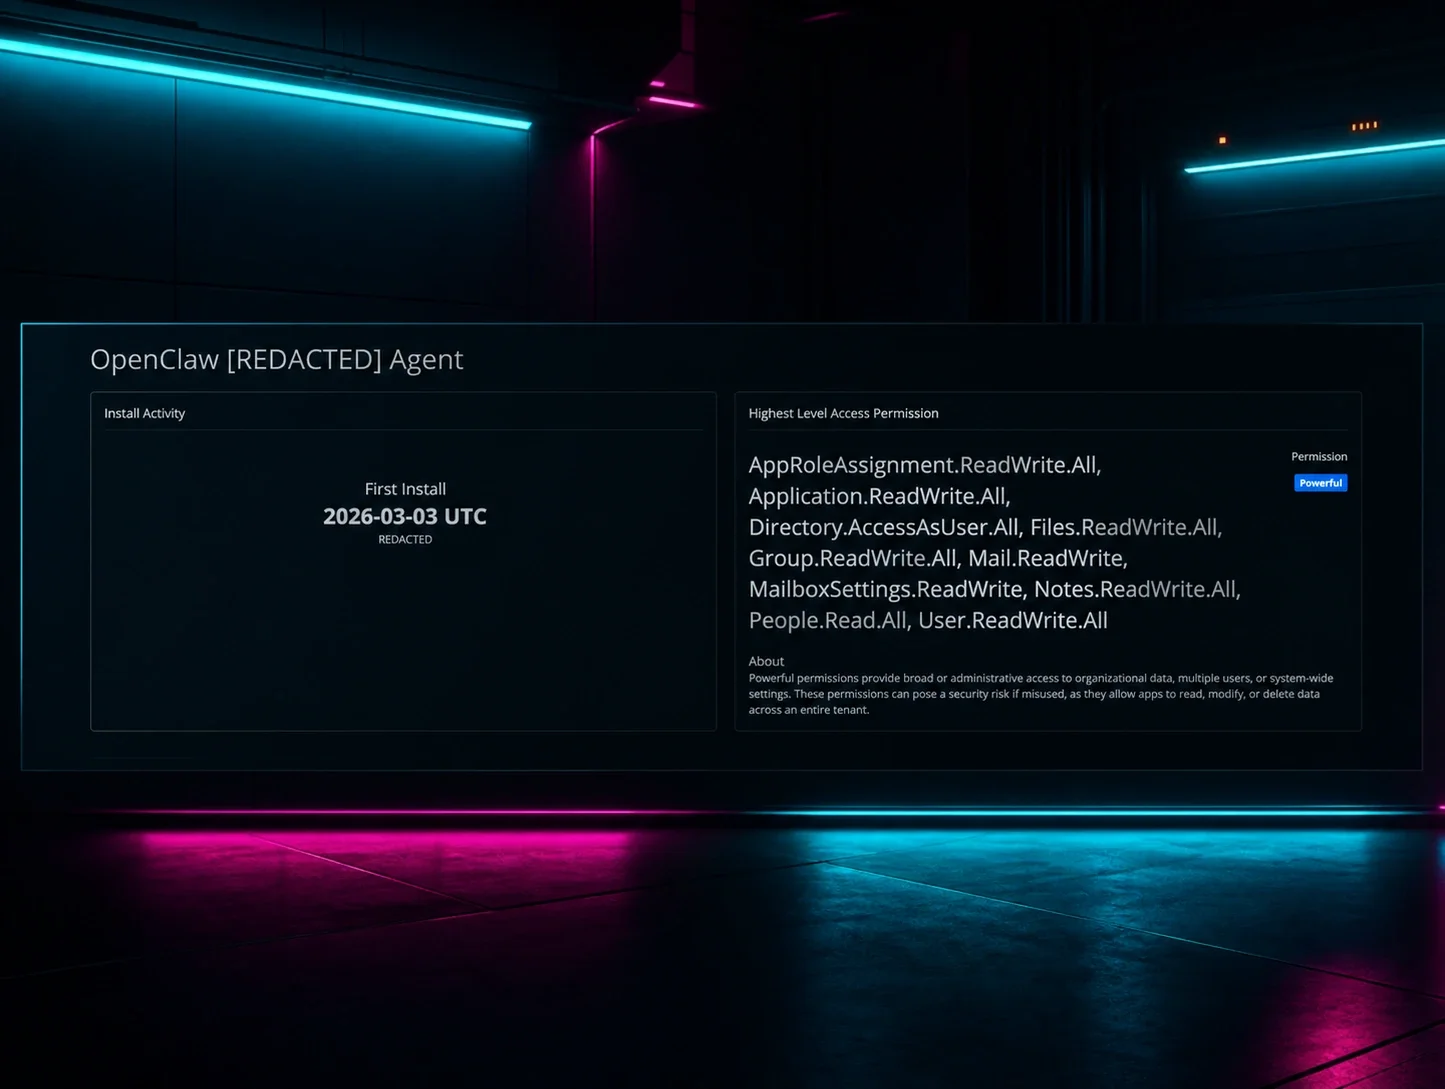
Huntress analyzes how the OpenClaw AI agent (and its earlier branding, Moltbot) manifests as a cloud service principal inside Microsoft 365/Entra ID tenants, often granted sweeping application permissions like Directory.ReadWrite.All, Application.ReadWrite.All, DelegatedPermissionGrant.ReadWrite.All, and Sites.FullControl.All. The post shows real customer-tenant findings of both user-installed and centrally-registered "too-powerful" OpenClaw instances, and walks through hunting them using Huntress Rogue Applications inventory and Managed SIEM ESQL queries against Entra audit logs to trace consent, permission changes, and downstream mailbox/SharePoint access.
huntress.comwriteupAdded 3 Sep 2026, published 1 Apr 2026🛡️ Security - Threat Actors Abuse Railway.com PaaS as Microsoft 365 Token Attack Infrastructure
Huntress details a device-code phishing campaign hitting 340+ Microsoft 365 tenants across the US, Canada, Australia, New Zealand, and Germany since February 2026, in which attackers abuse Railway.com's clean-IP PaaS infrastructure to run OAuth device-code token replay at scale, bypassing MFA entirely. The campaign chains vendor URL-rewriter abuse (Cisco, Trend Micro, Mimecast), compromised sites, Cloudflare workers.dev phishing pages, and AI-assisted lure generation, and Huntress has attributed it to the EvilTokens Phishing-as-a-Service platform advertised via Telegram. The post includes IOCs (Railway CIDR ranges), Sentinel KQL hunting queries, and mitigation guidance (block Railway IPs, revoke refresh tokens, restrict device code flow, enable CAE).
huntress.comwriteupAdded 3 Sep 2026, published 23 Mar 2026🛡️ Security - #ShadyHacks with Kyle Hanslovan
Huntress CEO Kyle Hanslovan demonstrates a full modern account-takeover chain against Microsoft 365: buying stolen credentials on a dark web marketplace, using a ChatGPT-crafted phishing email with a fake SharePoint link to trigger a ClickFix-style CAPTCHA that tricks the victim into pasting a PowerShell command, stealing active session cookies with an infostealer, and importing them via the Cookie Editor browser extension to bypass MFA entirely. It then covers post-compromise tradecraft — malicious inbox rules to forward/hide sensitive emails, Teams-based social engineering of IT support to register new MFA devices, and abusing email-based password resets on non-SSO apps (payroll, CRM) — plus defensive recommendations (conditional access, inbox rule auditing, DMARC/DKIM/BIMI, session revocation processes, security awareness training).
huntress.comwriteupAdded 3 Sep 2026, published 26 Nov 2025🛡️ Security - Device Code Phishing: OAuth 2.0 Attacks in Google & Azure
A Huntress researcher walks through Device Code Phishing, an OAuth 2.0 device authorization grant abuse technique, and shows why it is far more dangerous against Azure/Microsoft 365 than against Google Cloud. In Azure, the attacker controls the requested resource and can use Microsoft's undocumented "Family of Client IDs" (e.g. the Microsoft Authentication Broker client ID) to phish a Primary Refresh Token capable of joining rogue devices, enrolling MFA, and full account takeover; Google's device code implementation restricts the flow to a handful of narrow scopes (GDrive file access, YouTube read-only) and requires a registered/verified OAuth app, neutering the same attack. The piece includes working curl/Python requests for both providers and references prior research by Dirk-jan Mollema, Nestori Syynimaa, and Lina Lau.
huntress.comwriteupAdded 3 Sep 2026, published 6 Feb 2025🛡️ Security - DMARC Identifier Alignment: relax, don't do it, when you want to go to it
A practical walkthrough showing how a dangling DNS CNAME (subdomain takeover) combined with the default 'relaxed' DMARC alignment mode (aspf=r/adkim=r) lets an attacker send phishing emails that pass SPF and DMARC for the victim's organizational domain, using a self-owned mail server behind Microsoft 365. The author also demonstrates a partial DKIM trick — signing with a domain other than the spoofed sender to make emails look more legitimate — and shows the resulting mail landing in an Outlook inbox with dmarc=pass. It recommends setting aspf=s/adkim=s (strict alignment) and cleaning up unused DNS records as mitigations.
 bencteux.frwriteupAdded 3 Sep 2026, published 25 Jan 2023🛡️ Security