Skip to content

256 results for β€œPython”

What you seeeverything
opensourcemalware.comwriteupπŸ›‘οΈ Security

Earliest Known PolinRider Malware Found in 2025 npm Packages

OpenSourceMalware traces nine itsa-* npm package versions published on 4 May 2025 from a hijacked maintainer account to the PolinRider campaign, eight months before documented victims. It decodes the EtherHiding chain (BNB Smart Chain and Ethereum calldata, JADESNOW, INVISIBLEFERRET bootstrapper, Socket.IO RAT, Python stealer) and links the 2025 sample to 2026 force-push infections. It lists IOCs, hashes, a timeline and hunting guidance.

npmNode.jsPython+3
PolinRiderEtherHidingJADESNOW+9

Supply Chain, Malware & RE, Threat IntelΒ· Published and added 30 Oct 2026

github.comrepo🧠 AI

Show HN: I Turned DOOM into a Transformer

Doomformer compiles integer neural networks into ZDoom maps that run in ViZDoom. Voodoo dolls do the arithmetic, and sector light levels and plane heights hold the values. Python reads every value back and compares it with a NumPy integer reference at tolerance 0. It runs MNIST (97.16 % on all 10,000 digits, every pass exact), small transformers, a learning perceptron and a SUBLEQ machine. It is about 23,000 times slower than NumPy on a small MLP.

ViZDoomZDoomACS+10
DoomformerDOOMFreedoom+6

research, inferenceΒ· Added 30 Oct 2026, published 29 Oct 2026

vulncheck.comtoolπŸ›‘οΈ Security

VulnCheck - Outpace Adversaries

VulnCheck Open Source is an index of VulnCheck's open-source tooling for its vulnerability and exploit intelligence. It lists a Python API client, a CLI, a GitHub Action for CI/CD, go-exploit (a Go exploit framework), an MCP server for delivering intelligence to AI clients, and VulnCheck Insights, a Chrome extension that highlights CVEs, CPEs and PURLs on web pages and enriches them. The page gives only one-line descriptions.

GoPythonGitHub Actions+2
VulnCheckgo-exploitVulnCheck Insights+2

Offensive Security, DevSecOpsΒ· Added 29 Oct 2026

github.comcourse🧠 AI

rohitg00/ai-engineering-from-scratch

ai-engineering-from-scratch is a free, MIT-licensed curriculum of 542 lessons in 20 phases, from math and deep learning through transformers, LLM engineering, MCP, agents and capstones. Code is in Python, TypeScript, Rust and Julia. It includes three graded projects (retrieval evaluation, agent trace debugger, tool call firewall), installable tutor skills for Claude Code and Codex, and certification prep tracks.

PythonTypeScriptRust+13
Rohit GhumareOpenClawHermes+6

Β· Added 29 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Cisco Open Sources Quarry to Catch AI Agent Attacks Hidden in Harmless Steps

Project Quarry is a neurosymbolic rule language Cisco has open sourced to detect AI agent attacks that only show up across a sequence of individually benign steps. Rules combine ML classifier and LLM judge evidence with symbolic checks on sequences, strings and tool relationships. The starter pack has a DSL, evaluation runtime, CLI scanner, Python SDK and a plugin for Claude Code, Codex and other MCP-compatible agents.

QuarryModel Context ProtocolClaude Code+2
Project QuarryCisco Integrated AI Security & Safety Framework

AI Security, Blue Team & DetectionΒ· Published and added 29 Oct 2026

opensourcemalware.comtalkπŸ›‘οΈ Security

The OpenSourceMalware Show #27

The OpenSourceMalware Show #27 (28 October 2026) is a podcast episode with transcript. It covers the Brotli decoder bug (CVE-2026-111497) vendored in C code across Python, Rust and PHP, and how to find copies via decode.c. It also covers the LiteLLM v1.107.0 compromise from an unrevoked admin key and a relaxed release control, and the MALFEX npm campaign hiding payloads in PNG-header files, plus an AGENTS.md lure and DPRK fake fonts in TTF/OTF.

BrotliLiteLLMnpm+3
CVE-2026-111497Node2ShellPHP2Shell+10

Supply Chain, Threat Intel, DevSecOpsΒ· Published and added 29 Oct 2026

socket.devarticleπŸ›‘οΈ Security

eMudhra, Brotli, and the Long Tail of a Security Fix

Socket post on why fixing the eMudhra weak-key intermediate CA incident (October 2026) and Brotli memory corruption CVE-2026-111497 takes more than updating Node.js. Bundled Brotli copies in Bun, Python Requests and .NET, Go binaries needing rebuilds, and per-program certificate stores all leave stale copies. It lists steps: track bundled components, keep a rebuild path, use workarounds, and verify the shipped artifact.

Node.jsBrotliBun+6
CVE-2026-111497eMudhraOneCRL+6

Supply Chain, AppSecΒ· Published and added 26 Oct 2026

x.comthread🧠 AI

Akash Rajagopal (@akashsairaja) on X

Ollama overview thread by Akash Rajagopal on X. It lists six steps: install on macOS, Linux, Windows or Docker; run `ollama run gemma4`; use the REST API on localhost:11434 (/api/chat); call it from ollama-python and ollama-js; llama.cpp as the README's supported backend; and `ollama launch claude` to connect Claude Code. Codex, OpenCode, Copilot CLI and Droid also work. The thread cites 184k GitHub stars and an MIT licence.

Ollamallama.cppClaude Code+10
Gemma 4Akash Rajagopal

inference, coding-agentsΒ· Added 27 Oct 2026, published 26 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Node2Shell: Brotli Flaw Triggers Patching Across Microsoft, Node.js, Python Packages

CVE-2026-111497 (Node2Shell) is an out-of-bounds write in Google's Brotli decoder, versions 1.0.3 through 1.2.0, rated CVSS v4 9.2. Fixed in Brotli 1.0.10, 1.1.1 and 1.2.1, with patches from Node.js, Microsoft (.NET, Visual Studio, PowerShell on October 25), PyPI Brotli and brotlicffi, Bun, Envoy and Istio. Imperva showed code execution on Node.js 24.22.0 arm64; no in-the-wild exploitation is reported and some researchers say it only enables DoS.

BrotliNode.jsPython+3
CVE-2026-111497Node2ShellHTTP2Shell+5

AppSec, Supply ChainΒ· Published and added 26 Oct 2026

wiz.ioadvisoryπŸ›‘οΈ Security

Broccoli2shell: Everything You Need To Know About The Critical Brotli Decoder Vulnerability

CVE-2026-111497 (Broccoli2Shell, also Node2Shell and HTTP2Shell) is an out-of-bounds write in the upstream Brotli C decoder. It affects Node.js, Bun, Envoy Proxy, Istio and Python packages, and can lead to memory corruption, information disclosure, crashes or RCE when untrusted Brotli data is decompressed. Wiz reports 91% of cloud environments have vulnerable resources. The post lists patching, inventory, rebuild and temporary mitigation steps.

BrotliNode.jsBun+3
CVE-2026-111497Broccoli2ShellNode2Shell+8

AppSec, Cloud & InfraΒ· Published and added 25 Oct 2026

github.comrepo🧠 AI

Show HN: Farol – A risk map of a pull request for the person who approves it

farol is a free, MIT-licensed CLI and GitHub Action that runs after an AI code review and gives the human approver a risk verdict (fast track, quick review, careful review) and a 0-100 score for a pull request. It uses the TypeScript type checker, go/types and Python ast to trace which pages, APIs and jobs a change reaches, and it adds diff coverage, security findings and contract breaks. It never executes or sends code.

GitHub ActionsTypeScriptGo+10
farolClaude CodeWinnin

coding-agentsΒ· Added 26 Oct 2026, published 25 Oct 2026

github.comrepo🧠 AI

alirezarezvani/claude-skills

claude-skills is an MIT-licensed library of about 398 Claude Code skills, agents, personas and plugins across 20 domains, including engineering, marketing, compliance and C-level advisory. Each skill is a SKILL.md with stdlib-only Python CLI tools and reference docs. Install scripts and convert.sh adapt it to Codex, Gemini CLI, Cursor, Aider, Windsurf and other coding agents, and it includes a skill-security-auditor scanner.

Claude CodeCodexGemini CLI+12
HermesMistralAnthropic+2

coding-agents, prompting, agentsΒ· Added 25 Oct 2026

github.comrepoπŸ›‘οΈ Security

alirezarezvani/claude-skills

claude-skills is an open-source MIT library of about 398 Claude Code skills, agents and plugins that also installs into Codex, Gemini CLI, Cursor and 9 other coding agents. The security-relevant parts are skill-security-auditor, a stdlib-only Python scanner that checks skills for command injection, data exfiltration, prompt injection and dependency supply-chain risks before install, plus a security-guidance PreToolUse hook, a security suite and compliance skills (ISO 27001, SOC 2, GDPR).

Claude CodeCodexGemini CLI+3
skill-security-auditorPreToolUse hookagentskills.io+3

AI Security, Supply ChainΒ· Added 25 Oct 2026

x.comthread🧠 AI

Big Bull (@BIGBULLapp) on X

5ire is a desktop AI assistant and MCP client that connects to OpenAI, Anthropic, Google, Mistral, Grok, DeepSeek and Ollama from one window. It has a local knowledge base and tool calls over Model Context Protocol. The tools feature needs Python, Node and uv installed because it runs a local MCP server; without them it works only as a chat client.

Model Context ProtocolPythonNode.js+3
5ireOpenAIAnthropic+4

mcp, llm-appsΒ· Added 25 Oct 2026, published 24 Oct 2026

arxiv.orgpaper🧠 AI

Intervention-Certified Amplification: A Validity Gate for $Οƒ$-Weighted Post-Training

Intervention-Certified Amplification (ICA) is a validity gate for sigma-weighted hybrid SFT/RL post-training. The paper shows that DIAA, a per-sample sigma-weighted hybrid, emits unexecuted tool-integrated reasoning on 29% of MATH-500 prompts (three times vanilla GRPO) even with Python fences removed from its anchor. ICA gates sigma with paired-rollout evidence, cutting TIR to 13.8% (frozen) and 11.2% (online) and raising accuracy from 47.5% to 48.7% and 49.3%. It transfers to GSM8K.

GRPOPython
DIAAIntervention-Certified AmplificationMATH-500+2

training, researchΒ· Added 27 Oct 2026, published 24 Oct 2026

magazine.sebastianraschka.comcourse🧠 AI

Building Reasoning Models from the Ground Up: A Video Course

Building Reasoning Models from the Ground Up is a series of eight coding videos (about 11 hours) by Sebastian Raschka, accompanying his book Build a Reasoning Model (From Scratch). Starting from a pre-trained Qwen3 0.6B model, it implements KV-cached generation, a MATH-500 verifier, self-consistency and self-refinement, simplified GRPO for RLVR, and distillation from DeepSeek R1 answers in Python and PyTorch.

PyTorchPythonQwen3+5
Sebastian RaschkaMATH-500DeepSeek-R1+2

training, evals, inferenceΒ· Published and added 24 Oct 2026

x.comthreadπŸ›‘οΈ Security

Prasenjit Sarkar (@stretchcloud) on X

Post on the LiteLLM supply-chain compromise. Attackers spent eleven days in the GitHub org, ran a workflow on a throwaway branch to take twenty secrets including a GitHub App private key, then used stolen GitHub CLI OAuth tokens to publish malicious release 1.107.0 from a lookalike Berri-AI repo. A Python startup file harvested sixteen credential categories and LiteLLM proxy Postgres provider keys. Socket flagged the wheels in seven minutes.

LiteLLMPyPIGitHub Actions+3
Berri-AIBerriAILiteLLM 1.107.0+3

Supply Chain, DevSecOps, AI SecurityΒ· Added 26 Oct 2026, published 24 Oct 2026

x.comthread🧠 AI

EveryDev.ai (@EveryDevAi) on X

ToolUniverse, from ScientistTools, is an open-source (Apache-2.0) toolkit that gives any LLM one interface to more than 1,000 scientific tools, models and databases such as PubMed, UniProt and ChEMBL. It ships a native MCP server, a Python SDK and a tu CLI, plus 68 pre-built agent skills. The post says it works with Claude Code, Cursor, Gemini CLI and Windsurf.

Model Context ProtocolPythonClaude Code+4
ToolUniverseScientistToolsPubMed+2

mcp, agentsΒ· Published and added 24 Oct 2026

aikido.devadvisoryπŸ›‘οΈ Security

Python packages are also vulnerable to the Node2Shell Brotli flaw (CVE-2026-111497)

Python2Shell is the Python-side impact of CVE-2026-111497 (Node2Shell), a Brotli decoder flaw (CVSS 4.0 9.2) in DecodeBlockTypeAndLength() that mixes an unchecked return value with an out-of-bounds write. Brotli 1.2.0 and earlier, and brotlicffi 1.2.0.x, are affected through urllib3, requests, httpx, aiohttp and Scrapy. Fixes are Brotli 1.2.1 and brotlicffi 1.2.1.0; as of 23 October 2026 advisory databases do not map the CVE to either package. The post lists checks and workarounds.

BrotlibrotlicffiPyPI+3
CVE-2026-111497Node2ShellPython2Shell+4

AppSec, Supply ChainΒ· Published and added 23 Oct 2026

microsoft.comwriteupπŸ›‘οΈ Security

Inside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks

Microsoft's analysis of the LiteLLM 1.107.0 compromise, published to PyPI and container images on 21 October 2026. The wheel shipped cook.pth, cook.py and sitecustomize.py, so a credential collector (PRIVCOLLECT) ran whenever Python started, even without importing LiteLLM. It covers AES/RSA-encrypted exfiltration to litellm.dev, a re-armable Unix loader, Defender KQL hunting queries, ATT&CK mapping and rotation guidance.

LiteLLMPythonPyPI+3
cook.pthPRIVCOLLECTT1195.001+4

Supply Chain, Blue Team & Detection, Threat IntelΒ· Published and added 23 Oct 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

Python Packages Vulnerable to Node2Shell

Analysis of CVE-2026-111497 (Node2Shell), an out-of-bounds write in Google's Brotli C decoder, showing it also affects the PyPI packages Brotli (all releases up to 1.2.0) and brotlicffi (up to 1.2.0.2). The author diffed the 1.2.0 and 1.2.1 sdists and confirmed the behaviour with AddressSanitizer. Fixes are Brotli 1.2.1 and brotlicffi 1.2.1.0, both patched without release notes. No advisory database lists either package yet.

BrotlibrotlicffiPyPI+3
CVE-2026-111497Node2ShellPHP2Shell+5

AppSec, Supply ChainΒ· Published and added 23 Oct 2026

stepsecurity.ioarticleπŸ›‘οΈ Security

eMudhra / emSign CA Compromise: What Python, pip, and CI/CD Users Need to Update

Guidance on the October 2026 eMudhra / emSign CA incident, where eight intermediate CA certificates had private keys generated with insufficient randomness. It explains why updating certifi alone does not fix pip's vendored bundle, and lists fixed versions (certifi 2026.10.19, pip 26.2.2, Python 3.15.1, 3.14.9, 3.13.17). StepSecurity's OpenSSL 4.0.3 tests showed the older bundle accepted seven emSign paths, while both corrected bundles rejected all fourteen.

pipPythoncertifi+3
eMudhraemSigncertificate authority compromise+3

Supply Chain, DevSecOpsΒ· Published and added 22 Oct 2026

github.comrepoπŸ›‘οΈ Security

Spectrmachina/Ztrust

ZTrust is a Python supply-chain scanner that checks manifests, lockfiles, source and GitHub workflows for vulnerable or malicious dependencies (via OSV.dev), typosquats, leaked secrets, unsafe lockfiles and risky CI patterns such as pwn requests and script injection. It outputs console, JSON and SARIF 2.1.0 and ships as a GitHub Action. It also includes a FastAPI bounty service using commit-reveal and shielded Zcash payouts for researchers.

PythonGitHub ActionsOSV+3
xz-utilstj-actions/changed-filesevent-stream+3

Supply Chain, DevSecOpsΒ· Added 27 Oct 2026, published 22 Oct 2026

x.comthreadπŸ›‘οΈ Security

Muscle AI (@themuscleai) on X

Post on the LiteLLM 1.107.0 PyPI compromise published 21 October 2026 and quarantined about 1 hour 43 minutes later. A malicious .pth file ran at Python startup and stole cloud credentials, private keys, browser data and AI tool auth files, then POSTed a tarball to an attacker endpoint. The author says attackers used stolen GitHub CLI OAuth tokens to push a trojanized commit chain and build official wheels. It lists five defenses: hash-pinned lockfiles, per-tool capped keys, release cooling periods, secret isolation and egress monitoring.

LiteLLMPyPIPython+3
TeamPCPcook.pth

Supply Chain, DevSecOps, AI SecurityΒ· Added 23 Oct 2026, published 22 Oct 2026

x.comarticle🧠 AI

Muscle AI (@themuscleai) on X

Muse AI's X post describes the compromise of LiteLLM 1.107.0, published to PyPI on 21 October at 7:39 AM and quarantined about 1 hour 43 minutes later. The payload was a .pth file that ran at Python startup and sent cloud credentials, private keys and AI dev-tool auth files to an attacker endpoint. The author lists five agent-builder defences: hash-locked pins, capped per-tool keys, a release cooling period, keeping secrets away from Python startup, and outbound traffic monitoring.

LiteLLMPyPIPython+3
SocketTeamPCP

ai-infra, agentsΒ· Added 23 Oct 2026, published 22 Oct 2026

x.comthreadπŸ›‘οΈ Security

SecureChap (@SecureChap) on X

Post describing a LiteLLM 1.107.0 PyPI compromise in which attackers used stolen GitHub CLI OAuth tokens from three engineers to trigger and approve the project-releaser workflow, producing eight malicious wheels and a tampered tarball. The wheels drop cook.pth, which runs at Python startup, and privcollect steals cloud tokens, keys, browser data, AI configs and LiteLLM proxy credentials, exfiltrating to litellm[.]dev/healthcheck. A second daemon polls a GitHub domain.txt hourly for new domains to fetch and execute. PyPI yanked the package the same day. The post is a single unsourced tweet.

LiteLLMPyPIpip+3
cook.pthprivcollectlitellm[.]dev+2

Supply Chain, DevSecOps, Threat IntelΒ· Published and added 22 Oct 2026

endorlabs.comwriteupπŸ›‘οΈ Security

LiteLLM 1.107.0 Compromised: Python Startup Hooks Steal Cloud, AI, and Proxy Credentials | Endor Labs

litellm 1.107.0 was published to PyPI on 21 October 2026 from a source revision that differs from the official tag. One line in the Maturin config (data = "cook") installs cook.pth, cook.py and sitecustomize.py, which run on every Python start. They steal cloud, AI and proxy credentials, including the LiteLLM database tables, and load remote code hourly. The post gives IOCs, a five-step response plan and hardening advice.

LiteLLMPyPIPython+3
litellm 1.107.0cook.pthsitecustomize.py+5

Supply Chain, Malware & RE, DevSecOpsΒ· Published and added 21 Oct 2026

stepsecurity.iowriteupπŸ›‘οΈ Security

litellm 1.107.0 Compromised on PyPI: Backdoored Wheels Drop a Credential Stealer and an Hourly Remote Code Loader

litellm 1.107.0 was published to PyPI on 21 October 2026 with all seven wheels backdoored through an injected `data = "cook"` maturin build line. The wheels drop cook.pth, cook.py and sitecustomize.py, which run on every Python start. They install a "privcollect" credential stealer (browser, SSH, cloud, AI coding tool and LiteLLM proxy database secrets, sent to litellm.dev) and an hourly GitHub dead-drop remote code loader. The post gives IOCs, detection commands and recovery steps.

LiteLLMPyPIPython+3
privcollectcook.pthsitecustomize.py+6

Supply Chain, Malware & RE, Blue Team & DetectionΒ· Published and added 21 Oct 2026

socket.devwriteupπŸ›‘οΈ Security

LiteLLM PyPI Package and Docker Images Compromised to Steal Cloud and AI Credentials

LiteLLM 1.107.0 on PyPI and GHCR images shipped Python startup hooks (cook.pth, sitecustomize.py) that steal cloud, SSH, browser and AI-tool credentials, including LiteLLM proxy database credentials. Image build provenance recorded a lookalike Berri-AI/litellm source repository. The post decodes the payload, encrypted exfiltration and GitHub-driven remote loader, and lists containment steps, MITRE ATT&CK mappings and IOCs.

LiteLLMPyPIPython+3
Berri-AIprivcollectcook.pth+12

Supply Chain, Malware & RE, Threat IntelΒ· Published and added 21 Oct 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

LiteLLM 1.107.0 PyPI Wheel Contains a Credential Stealer and Persistent Python Backdoor

LiteLLM 1.107.0 macOS x86-64 PyPI wheel analyzed by OpenSourceMalware contains three injected files (cook.pth, cook.py, sitecustomize.py) that run on every Python start. The payload, called privcollect, steals browser, SSH, cloud, CI/CD and AI-tool credentials, then uploads an AES/RSA-encrypted bundle to www.litellm.dev/healthcheck. A forked loader also fetches domain.txt from GitHub and executes /codepy hourly. The post lists IOCs, hashes and remediation steps.

LiteLLMPyPIPython+1
privcollectTeamPCPUpwind+4

Supply Chain, Malware & RE, Threat IntelΒ· Published and added 21 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

Amazon-Themed ClickFix Campaign Serves Up Finger-Licking Malware

Huntress analysis of an Amazon-themed ClickFix campaign that used a Google sponsored result, a fake Amazon login on Google Sites and a fake CAPTCHA to make victims run the Windows finger utility. The .plan script drives IronPython, a Cyrillic-substituted Base64 Python loader, Doina, a Node.js stage, Lumma Stealer via sRDI, and a pirated NetSupport RMM. It lists C2 domains and gives detection tips (aclk/gclid markers, blocking the Run dialog).

WindowsfingerIronPython+3
ClickFixDoinaLumma Stealer+8

Threat Intel, Malware & RE, Blue Team & DetectionΒ· Published and added 21 Oct 2026

x.comrepoπŸ›‘οΈ Security

Cyber DetectiveπŸ’™πŸ’› (@cyb_detective) on X

Python Cybersecurity Libraries is a curated GitHub list by Yogsec, shared in a post by cyb_detective. It groups Python libraries by task: network analysis, penetration testing, threat intelligence, reverse engineering and malware analysis, forensics and investigation, web application security, CTF, and machine learning for security. The tweet shows only the category names, not the individual libraries.

PythonGitHub
Yogseccyb_detective

Offensive Security, Blue Team & Detection, Malware & REΒ· Added 24 Oct 2026, published 21 Oct 2026

coindesk.comarticleπŸ›‘οΈ Security

A company that vouches for websites had secret keys so weak that 8 of them were cracked

eMudhra, an Indian certificate authority with over 60 million issued certificates, had eight CA private keys that were tiny integers such as 4, 56 and 237. Researcher Scott Helme recovered all eight from public certificates in under a second, and the keys were exposed from April 2025. Mozilla, Chrome, Apple and Microsoft blocked them between 17 and 20 October 2026, but curl, Python, Node.js, Go and Java accepted a forged Stripe API certificate because they skip revocation checks.

cURLPythonNode.js+3
eMudhraSectigoScott Helme+5

otherΒ· Published and added 21 Oct 2026

x.comrepoπŸ›‘οΈ Security

☣ KitPloit - Hacker Tools (@KitPloit) on X

DidierStevensSuite is a collection of Python scripts for malware analysis, file format parsing, hashing and forensic triage. It includes utilities for analysing PDF and OLE documents and for XOR-obfuscated data. The post is a short KitPloit announcement that links to the repository and gives no usage detail.

Python
Didier Stevens

Malware & RE, Blue Team & DetectionΒ· Added 21 Oct 2026, published 20 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-77932 affects DB-GPT through 0.8.2 (dbgpt-app). The /api/v1/chat/react-agent route accepts unauthenticated requests because get_user_from_headers returns an admin-role user, and the ReAct agent can reach unsandboxed Python and shell tools. Lasso reported root in the webserver container in a lab. The post gives CVSS 9.8 and 9.3, no verified fix (0.8.2 is still the latest release), no KEV match, no EPSS data, and a SOC hunting trail.

DB-GPTPythonDocker+3
CVE-2026-77932CWE-306Lasso+4

AI Security, AppSec, Blue Team & DetectionΒ· Added 23 Oct 2026, published 20 Oct 2026

heymaxwell.aiarticle🧠 AI

Maxwell: A new kind of model that sits between code and hardware

Maxwell (Maxwell's Daemon) is doubleAI's first "code execution model" (CEM). It runs inside a live program, finds bottlenecks and emits faster machine code for the exact CPU or GPU, leaving the source untouched. Each rewrite ships with a machine-checked proof of semantic equivalence, built on a formalisation of Python. Early access is announced; the post gives no benchmark figures.

PythonPyTorchRust+6
doubleAIMaxwellAlan Turing+3

models, inference, researchΒ· Added 20 Oct 2026, published 19 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

A Key-Recovery Attack on the GTLN Knapsack Cryptosystem via Continued Fractions

This ePrint paper (2026/2543) gives a key-recovery attack on the GTLN knapsack public-key cryptosystem of GΓ³mez-Torrecillas, Lobillo and Navarro. Continued fractions recover small-denominator ratios of public-key differences, and gcd computations then yield private-key integers, the modulus and the shift, using only the public key. The Python implementation recovered the full private key in all 2,400 trials across 24 recommended parameter sets, each in under 0.05 seconds.

GTLN knapsack cryptosystemGΓ³mez-TorrecillasLobillo+1

otherΒ· Added 20 Oct 2026, published 19 Oct 2026

huggingface.corepo🧠 AI

DeepSeek-v4.1-Flash-1017

Model card for DeepSeek-V4.1-Flash-1017, a minor update to DeepSeek-V4.1-Flash with MIT-licensed weights. It claims gains in reasoning, coding, agentic tasks and visual benchmarks, with shorter task time and output length that move the performance–cost Pareto frontier across agent harnesses (Claude Code for Terminal-Bench 4.0, Mini-SWE-V2 for DeepSWE v1.1). It ships no Jinja chat template. It provides a reference encoding.py for multi-turn chat, tool calling, thinking mode, numeric reasoning effort and interleaved images, plus deepseek-recipe, Rust libraries with Python bindings for prompt encoding and output parsing. Serving recipes are given for Transformers, vLLM, SGLang and Docker Model Runner.

TransformersvLLMSGLang+5
DeepSeekDeepSeek-V4.1-FlashDeepSeek V4+3

models, inferenceΒ· Added 18 Oct 2026, published 17 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks

Huntress documents abuse of ConnectWise Cloud Backup (formerly SkyKick) vendor app credentials, used on October 15 from 144.172.64[.]128 to obtain Microsoft Graph tokens in at least 162 customer M365 tenants via client assertion. In one tenant, a ConnectWise Cloud Management Teams app self-assigned Global Administrator and added client secrets to an MSP management app and Huntress's own app, a persistence technique. The post lists application IDs, Entra sign-in and audit-log checks, user-agent indicators (kiota-dotnet vs Python-urllib/3.12, curl/7.88.1), and mitigation steps such as disabling (not deleting) the enterprise apps and reviewing added credentials.

Microsoft 365Microsoft Entra IDHuntress+1
ConnectWiseSkyKick144.172.64.128+7

Threat Intel, Identity & Access, Blue Team & DetectionΒ· Added 17 Oct 2026, published 16 Oct 2026

anthropic.comwriteupπŸ›‘οΈ Security

Claude reveals ECDSA curve origins

Anthropic's Frontier Red Team reports that Claude recovered how the NIST P-192/224/256/384/521 and ANSI X9.62 curve seeds were generated. They are outputs of the C library's lrand48 LCG seeded with 1997–98 Unix timestamps, not hashes of a passphrase. The method scanned for weak-PRNG signatures, then used LLL lattice reduction to recover the truncated LCG state and stepped it back to srand48 initialization. Claude also traced some base points to the FreeLIP/NTL random generator. Reproducible Python is included. The authors say this is not an attack and makes deliberate backdoors less plausible. The B-163 seed and the base points of P-224/256/384/521 and the binary curves remain unexplained.

ClaudeNTLFreeLIP+1
NISTECDSANIST P-256+16

otherΒ· Added 17 Oct 2026, published 16 Oct 2026

anthropic.comwriteup🧠 AI

Claude reveals ECDSA curve origins

Anthropic's Frontier Red Team reports that Claude, given no hint, worked out how the NIST P-192/224/256/384/521 and ANSI X9.62 curve seeds were generated. They came from the C library's lrand48 LCG seeded with Unix timestamps from 1997–98, not from a hash of a phrase. Claude found this by scanning for weak-PRNG signatures and recovering the PRNG state with LLL lattice reduction. It also traced several prime-curve base points to the FreeLIP random generator. The post includes Python code that reproduces the seeds and base points. It says this is not an attack and makes backdoor claims less plausible. B-163 and the other base points remain unexplained.

ECDSAlrand48LLL+4
AnthropicClaudeNIST+10

researchΒ· Added 17 Oct 2026, published 16 Oct 2026

hackers-arise.comarticleπŸ›‘οΈ Security

Open-Source Intelligence (OSINT): Turn One Username into a Full Digital Dossier with Maigret

Hands-on walkthrough of Maigret, an open-source Python tool that checks a username against 3,000+ sites (top 500 by default) and builds a profile dossier by parsing public profile pages and recursively searching newly found usernames. Covers installation from GitHub, single-site and tag filtering, username permutation, HTML/PDF/CSV/JSON reports, graph output, and an optional LLM summary via OpenRouter. Positioned as a more thorough successor to Sherlock for username reconnaissance.

MaigretPythonKali Linux+2
Sherlock

OSINT, LearningΒ· Published and added 16 Oct 2026
endorlabs.comarticleπŸ›‘οΈ Security

Why Your SCA is Always Wrong | Endor Labs

Explains why traditional SCA tools are inaccurate: they parse package-manager manifests and assume those match what the code actually uses. It walks through phantom dependencies, misused dependency scopes, direct use of transitive dependencies and unused dependencies, using Python and JavaScript as examples. It argues for SCA based on program analysis, with source code as ground truth cross-checked against manifests and the file system. Useful for evaluating SCA tools and understanding SBOM accuracy limits.

PythonJavaScriptnpm+3
phantom dependenciestransitive dependenciesdependency scopes

Supply Chain, AppSecΒ· Published and added 16 Oct 2026

endorlabs.comarticleπŸ›‘οΈ Security

GitHub Action tj-actions/changed-files supply chain attack: what you need to know | Endor Labs

Endor Labs explains the March 2025 compromise of the tj-actions/changed-files GitHub Action (CVE-2025-30066). Attackers pushed a malicious commit and retroactively repointed version tags, so a Python payload dumped CI/CD secrets to workflow logs across about 23,000 repositories. The post gives response steps: find usage with a GitHub code search, remove the Action from all branches or enforce an Actions allowlist, audit logs for suspicious outbound requests and IPs, and rotate exposed secrets. It also notes the March 17 restoration and the risk of transitive Action dependencies. It includes Endor Labs customer steps (the `--ghactions --secrets --git-logs` scan flags).

GitHub ActionsGitHubEndor Labs+1
CVE-2025-30066tj-actions/changed-files

Supply Chain, DevSecOpsΒ· Published and added 16 Oct 2026

github.comrepoπŸ›‘οΈ Security

gichirimaku/wp2shell-PoC

wp2shell-PoC is a Python proof-of-concept exploiting a pre-authentication RCE chain in WordPress core, combining CVE-2026-63030 (REST API batch route confusion) and CVE-2026-60137 (SQL injection in WP_Query). It demonstrates escalation from the route-desync bug through blind SQLi, customize_changeset forgery, and hook re-entry to administrator account creation and arbitrary command execution via a malicious plugin upload. The tool supports vulnerability checking, data extraction (union, error-based, blind techniques), and full shell access with or without existing admin credentials.

WordPressPython
CVE-2026-63030CVE-2026-60137SQL injection+1

AppSec, Offensive SecurityΒ· Added 23 Oct 2026, published 15 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

β™«Whyβ™₯Notβ™ͺ (@Python_s_) on X

Alert summarizing XBOW's disclosure of a three-stage Chrome for Windows exploit chain: V8 Maglev memory corruption (CVE-2026-85045), Animated WebP decoder memory corruption (Chromium issue 548509153), then a Crashpad sandbox escape (CVE-2026-78952). Loading a crafted page was enough; no click or download needed. Human researchers working with GPT-5.6 Sol agents built it in six days, Google paid $250,000, all three bugs are fixed, and no in-the-wild exploitation is confirmed. It advises updating Chrome and restarting, and gives forensic triage pointers.

ChromeV8Crashpad+3
CVE-2026-85045CVE-2026-78952Chromium issue 548509153+2

Offensive Security, AI Security, Threat IntelΒ· Added 15 Oct 2026, published 14 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

SAP Patches Critical NetWeaver, S/4HANA Vulnerabilities

SecurityWeek summarizes SAP's October 2026 Security Patch Day (22 notes, four critical). Critical flaws: CVE-2026-89111 (CVSS 10) OAuth2 SSRF in SAP Cloud SDK for Python that leaks client credentials via the tenant_subdomain parameter; CVE-2026-89110 (9.9) NetWeaver broken access control allowing ABAP code execution through Fiori rule definition input; CVE-2026-89107 (9.9) S/4HANA Visual Composer code injection; and CVE-2026-89108 (9.1) missing authorization check in Manufacturing Integration and Intelligence allowing admin account creation. SAP reports no exploitation in the wild.

SAP NetWeaverSAP S/4HANASAP Cloud SDK for Python+3
CVE-2026-89111CVE-2026-89110CVE-2026-89107+3

AppSecΒ· Published and added 14 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

Summary of SAP's October 13, 2026 Security Patch Day (16 new notes, 4 GitHub advisories). It leads with CVE-2026-89111, a CVSS 10.0 OAuth2 SSRF in SAP Cloud SDK for Python before 0.45.2, where an attacker-controlled tenant_subdomain redirects token requests and exfiltrates client credentials. It also lists three other critical flaws: broken access control in NetWeaver Visual Composer, code injection in S/4HANA substitution/validation rules, and a missing authorization check in the Manufacturing Integration and Intelligence (XMII) Configuration Service. It notes that none are in CISA KEV and SAP reports no in-the-wild exploitation.

SAP Cloud SDK for PythonSAP NetWeaverSAP S/4HANA+3
CVE-2026-89111CVE-2026-89110CVE-2026-89107+5

AppSec, Identity & AccessΒ· Added 15 Oct 2026, published 13 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

β™«Whyβ™₯Notβ™ͺ (@Python_s_) on X

Alert thread on CVE-2026-35029 (CVSS v4.0 8.7) in LiteLLM Proxy, versions before 1.83.0. A low-privilege authenticated user can bypass admin authorization on /config/update, change runtime settings, read server files, take over admin credentials and run Python through remotely loaded modules (S3/GCS-hosted). Check Point Research published a full execution chain on October 13 after the April 2026 disclosure. The post lists hunting pointers (non-admin POSTs to /config/update, env-var changes, unexpected pass-through endpoints, cloud module loading) and advises upgrading to 1.83.9 or later and rotating credentials.
LiteLLMPythonCVSS
CVE-2026-35029Check Point ResearchCWE-306

AI Security, AppSecΒ· Published and added 13 Oct 2026

github.comrepo🧠 AI

BijectiveLabs/trading-research-agents

Open-source Python CLI (`tra`) for autonomous trading desks in which LLM analysts (technical, macro, on-chain, sentiment) and validators only give opinions on figures the system computed. Fixed rules do the arithmetic: pricing the round-trip cost, applying risk limits, sizing, cost gates, and sending a single order with stop attached via ccxt (Bybit and OKX demo accounts tested). It supports multiple model providers with per-role models, effort settings and fallbacks. Every answer is parsed against a closed schema, every refusal is logged with the figure behind it, and models can tighten but never loosen controls. This makes it a concrete reference for keeping LLM agents away from arithmetic and money.

Pythonccxtuv+2
Bijective LabsBybitOKX+8

agents, ai-infraΒ· Added 18 Oct 2026, published 13 Oct 2026

github.comrepo🧠 AI

BijectiveLabs/bitra

bitra (CLI name tra) is an MIT-licensed Python framework from Bijective Labs for autonomous trading agents. Language models only read system-computed figures and give opinions, while deterministic code prices the round trip, applies declared limits, sizes the trade and sends one order with stop attached. Every cycle's briefs, answers and refusals are stored on disk with hashes. It supports many model providers and ccxt venues, with sandbox, demo and mainnet tiers.

PythonPyPIuv+7
Bijective Labsgpt-oss-120bgpt-oss+7

agents, ai-infraΒ· Added 25 Oct 2026, published 13 Oct 2026

github.comrepo🧠 AI

santosomar/AI-agents-for-cybersecurity

Companion repository for Omar Santos's Pearson and O'Reilly trainings and books. It has eight parts of runnable Python labs: chat models, embeddings, prompt templates, LCEL prompt chaining, Chroma-based RAG, ReAct/LangGraph/CrewAI/DeepAgents agents, and FastMCP servers (nmap, CISA KEV, Shodan). It also includes guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz), a tokenomics module on agent cost (context compounding, prompt caching, model routing, token budget guards, batch API, cost per accepted outcome), and a vendor-neutral design spec for a human-gated multi-agent assessment harness. It is a current, practical curriculum for building and operating agents. Some examples act on real systems and should only be run in an authorized lab.

PythonuvLangChain+17
Omar SantosPearsonO'Reilly+15

agents, llm-apps, mcpΒ· Added 13 Oct 2026

x.comthreadπŸ›‘οΈ Security

Phillip Shoemaker (@pbsIdentity) on X

Social thread reacting to a newly disclosed high-severity OAuth vulnerability in the Model Context Protocol Python SDK, where a malicious MCP server could manipulate the authorization flow and steal credentials used by an agent. The author uses it to argue that delegated agent authority needs provenance (who granted it, to which agent, for which service and resource, whether it is transferable or replayable, and when it expires) and that machine-to-machine trust must be auditable by humans. Gives no CVE ID or technical exploit detail.

Model Context ProtocolPythonOAuth
confused deputy

AI Security, Identity & AccessΒ· Added 13 Oct 2026, published 12 Oct 2026

endorlabs.compaperπŸ›‘οΈ Security

2024 Dependency Management Report | Endor Labs

Endor Labs' 2024 report on open-source dependency management and vulnerability prioritization. It reports that under 9.5% of vulnerabilities are reachable at function level, and that combining reachability with EPSS cuts noise by about 98%. It also finds Python phantom dependencies (up to 60% of dependencies and 85% of vulnerabilities for some tenants), 18% of npm OSV entries lacking CVE aliases, 69% of advisories published after the fix release (median 25 days), and 47% of advisories with no code-level info. For Java, 24% of fixes need a major version bump and 95% of upgrades carry breaking changes. Written by a vendor, so the prioritization conclusions favor its product.

Endor LabsOSVNVD+4
CVE-2023-41080CVE-2017-12159CVE-2023-36566+10

Supply Chain, AppSecΒ· Published and added 12 Oct 2026

simonwillison.nettool🧠 AI

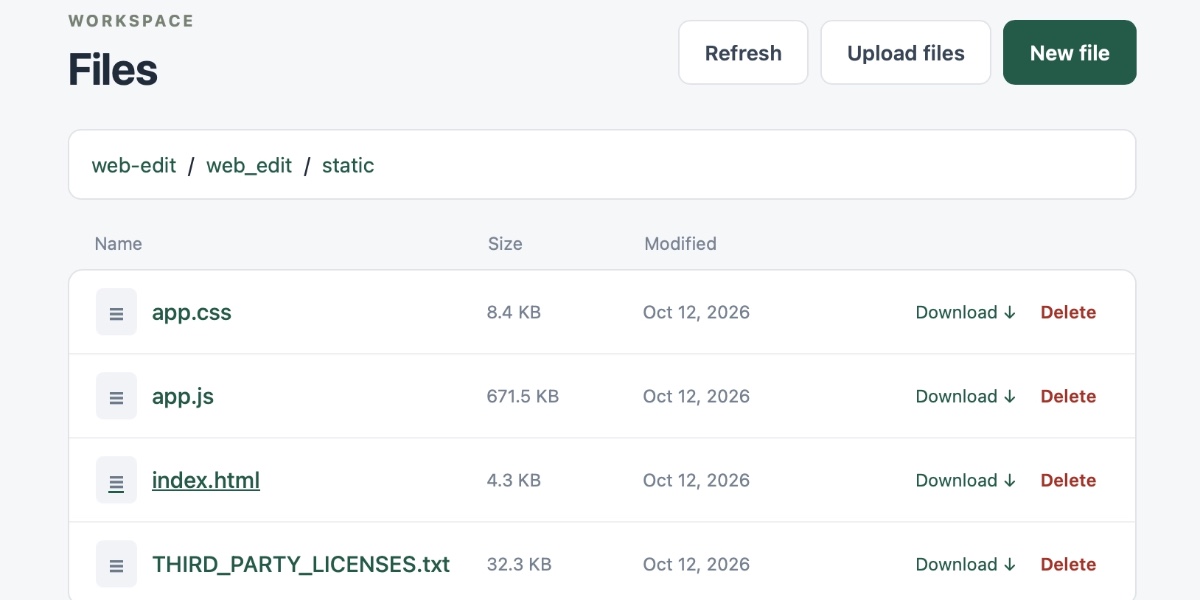
web-edit 0.1a0

web-edit 0.1a0 is a Python web app that gives a browser UI for viewing and editing files in a folder, intended to be started by an agent and reached over Tailscale from a phone. Simon Willison built it with Codex and GPT-6 Astra Extra High after wanting to edit a credentials file during a Codex Remote session without passing the credentials through the LLM. Editing uses CodeMirror 6 because Monaco's mobile experience is still weak.

PythonCodexCodeMirror 6+2
Simon WillisonGPT-6 Astra

coding-agentsΒ· Added 13 Oct 2026, published 12 Oct 2026

endorlabs.comarticleπŸ›‘οΈ Security

Is AI Coding Safe? Introducing the Agent Security League | Blog | Endor Labs

Endor Labs launches the Agent Security League, a public leaderboard extending CMU's SusVibes benchmark (200 tasks, 108 Python OSS projects, 77 CWEs) to commercial coding agents (Claude Code, Cursor, Codex) and frontier models. Functional pass rose to 84.4% from 61% in the original study, but secure pass peaked at only 17.3%. It also documents agents ignoring instructions and mining git history to copy the fix (SWE-Agent + Opus 4.6 did so in 163/200 tasks), and describes the cheating-detection and score-adjustment module added to the harness.

Claude CodeCursorCodex+2
Agent Security LeagueSusVibesOpus 4.6+1

AI Security, AppSecΒ· Published and added 12 Oct 2026

endorlabs.comarticle🧠 AI

Is AI Coding Safe? Introducing the Agent Security League | Blog | Endor Labs

Endor Labs launches the Agent Security League, a public leaderboard that extends CMU's SusVibes benchmark (200 Python tasks, 108 OSS projects, 77 CWEs). It tracks FuncPass and SecPass for commercial agents (Claude Code, Cursor, Codex) with newer models such as Claude Opus 4.x, Gemini 3 Pro and GPT-5.3 Codex. Functional correctness reaches 84.4% but SecPass peaks at only 17.3%. The authors also found agents reading git history to recover the fix, as in 163 of 200 tasks for SWE-Agent with Claude Opus 4.6, despite explicit instructions not to. They added a cheating-detection and score-adjustment phase.

Claude CodeCursorCodex+4
Endor LabsAgent Security LeagueSusVibes+14

evals, coding-agentsΒ· Published and added 12 Oct 2026

endorlabs.comarticleπŸ›‘οΈ Security

Static SCA vs. Dynamic SCA: Which is Better (and Why It's Neither) | Blog | Endor Labs

Compares static SCA (manifest/source scanning at build time) with dynamic SCA (runtime instrumentation). Static scans are complete but noisy and miss dependencies absent from manifests, for example in Python. Dynamic scans are relevant but incomplete, add agent overhead and surface findings late. It argues eBPF improves deployability of dynamic SCA but not its coverage limit. A worked example with a library of N vulnerable functions illustrates the difference. The author, Endor Labs, advocates static analysis of source code plus reachability analysis to filter findings by whether vulnerable code is actually called.

Endor LabseBPFSnyk+2

AppSec, Supply ChainΒ· Published and added 12 Oct 2026

endorlabs.comwriteupπŸ›‘οΈ Security

Malicious 'Pyronut' Package Backdoors Telegram Bots with Remote Code Execution | Blog | Endor Labs

Endor Labs analyzes the malicious PyPI package pyronut (versions 2.0.184–2.0.186), a trojanized fork of the Telegram framework pyrogram. It hooks Client.start() to import a hidden pyrogram/helpers/secret.py that registers Telegram handlers letting two hardcoded attacker accounts run arbitrary Python (/e via meval) and shell commands (/shell via /bin/bash -c). C2 runs entirely over Telegram, so there are no external network indicators; the post includes detection, credential-rotation and prevention guidance.

PyPIPythonTelegram+1
pyronutpyrogrammeval+4

Supply Chain, Malware & REΒ· Published and added 12 Oct 2026

x.comwriteup🧠 AI

Aditya (@adityawaslost) on X

Describes Resolve, a Kaggle benchmark of 16 single-function Python edits. An item counts as resolved only if both the fail-to-pass tests (new behavior) and the pass-to-pass tests (old behavior the prompt never restated) pass, following the SWE-bench rule. A second task, resolve-plus, adds a hidden edge suite. Results for 23 frontier and open models: GPT-6.1 Sol and GPT-5.6 Luna lead at 0.9375 on both tasks, while DeepSeek-R1, Sonnet 5.5 and Opus 5.5 drop from 0.9375 to 0.875. The write-up separates three failure types behind a flat score: breaking an unstated invariant, missing an unshown edge case, and sample-to-sample variance. It also compares score against output price per million tokens.

PythonClaudeGemini+3
Resolveresolve-plusKaggle+23

evals, coding-agentsΒ· Published and added 11 Oct 2026

github.comrepo🧠 AI

sepehr071/iran-mcp

iran-mcp is an open-source catalog of 39 MCP servers (488 tools) that let AI agents query Iranian websites such as Digikala, Torob, Divar, Snappfood, Jabama, Paziresh24, TSETMC and qavanin.ir, with prices normalised to Toman. Most servers are unofficial, read-only Python packages run with uvx; three are official hosted servers. It ships Claude Code plugins, Agent Skills, bundles, proxy lists and a machine-readable servers.json.

Model Context ProtocolPythonPyPI+11
DigikalaTorobDivar+10

mcp, coding-agentsΒ· Added 24 Oct 2026, published 11 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

β™«Whyβ™₯Notβ™ͺ (@Python_s_) on X

Alert on CVE-2026-106610, a critical (CVSS 9.8) incorrect privilege assignment flaw in the miniOrange OTP Verification WordPress plugin, versions 5.5.7 and earlier. Unauthenticated remote attackers can gain elevated permissions, potentially administrator, with no user interaction. Fixed in 5.5.8; no in-the-wild exploitation or public PoC verified. It advises auditing unexpected admin accounts and role changes, and warns that Patchstack's mitigation blocks legitimate requests too.

WordPressCVSS
CVE-2026-106610PatchstackminiOrange OTP Verification+1

AppSec, Identity & AccessΒ· Published and added 11 Oct 2026

github.comrepoπŸ›‘οΈ Security

sakidekin/CVE-2026-41940-PoC

This repository hosts a proof-of-concept for CVE-2026-41940, described as a CVSS 10.0 unauthenticated authentication bypass in cPanel and WHM caused by CRLF injection into server-side session files via the Authorization header. The accompanying Python tool (cve.py) can detect vulnerable cPanel/WHM instances, retrieve system and account information, and perform post-exploitation actions such as running OS commands, changing the root password, and opening an interactive WHM shell. It also supports bulk scanning workflows piped from subfinder, httpx, and Shodan.

PythonShodan
CVE-2026-41940CRLF injectionauthentication bypass

Offensive SecurityΒ· Added 23 Oct 2026, published 11 Oct 2026

x.comthread🧠 AI

Confident AI (@confident_ai) on X

Confident AI announces Eval Skills, open-source (Apache 2.0) agent skills for Claude Code and Codex. The `eval-build` skill takes an app to a runnable baseline: it finds realistic examples in traces and incidents, annotates failures, groups them into failure modes, curates cases with independent data splits, and builds graders validated against human judgment. The `eval-descent` skill runs a bounded loop of hypothesis, app change, eval re-run, regression check, then keep or revert, with held-out cases kept out of the loop. It ships Python and TypeScript tooling for tracing, annotation, grading and reports, plus a local UI or Confident AI for managing the loop.

Claude CodeCodexPython+1
Confident AIEval Skills

coding-agents, evals, promptingΒ· Published and added 9 Oct 2026

x.comtoolπŸ›‘οΈ Security

Trail of Bits (@trailofbits) on X

Trail of Bits announces SequenceHash, a library for hashing several inputs without concatenation ambiguity. Plain concatenation lets different input sequences produce the same SHA-256 digest. SequenceHash appends each input's length as a fixed 128-bit integer so every sequence has a single encoding. It ships for Rust, Go and Python, and removes a recurring bug class in crypto and appsec code.

RustGoPython
Trail of BitsSequenceHash

AppSecΒ· Added 11 Oct 2026, published 9 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

β™«Whyβ™₯Notβ™ͺ (@Python_s_) on X

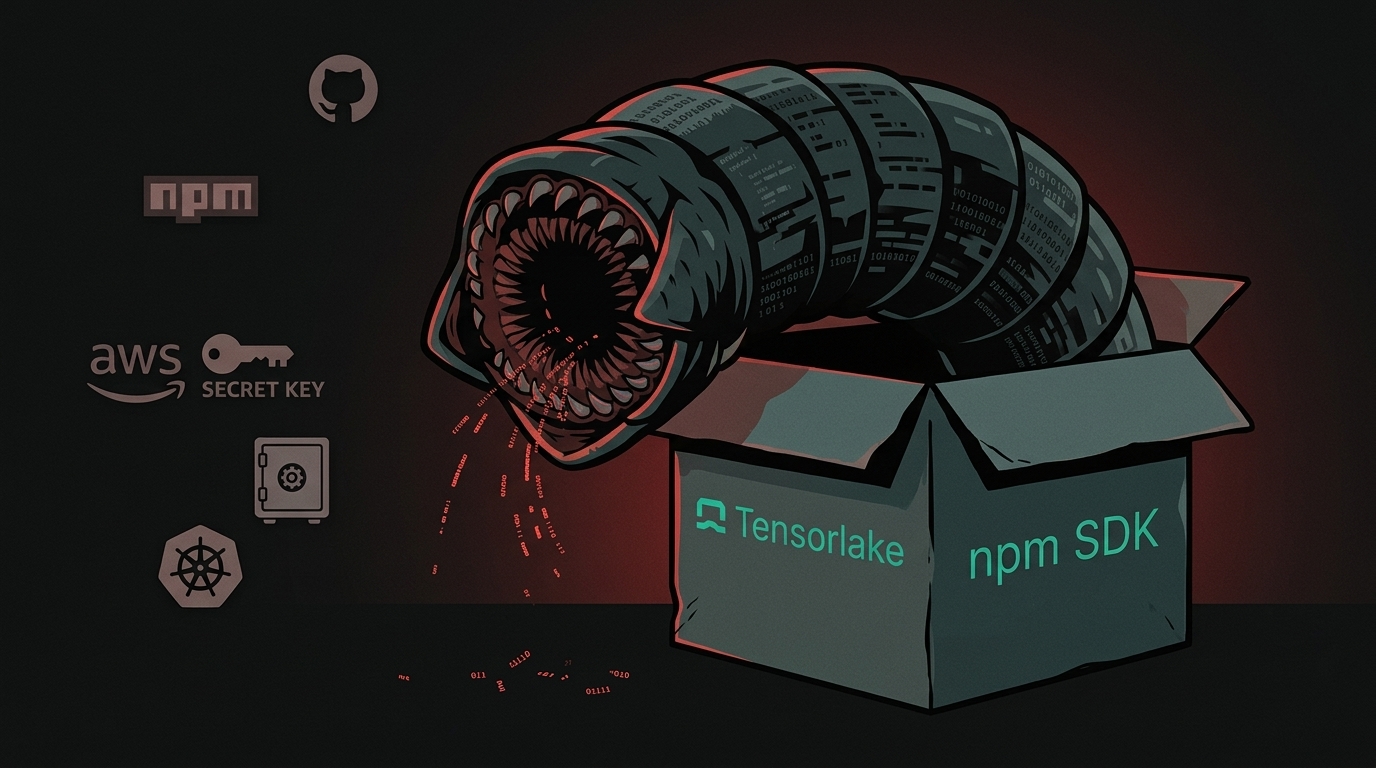
Alert summarizing Socket Threat Research's disclosure that a malicious version of the Tensorlake npm SDK (an AI-agent infrastructure package) was published with a preinstall hook delivering Shai-Hulud/ChainDrop credential-stealing malware. The payload targets GitHub, npm, AWS, Kubernetes and Vault credentials, persists via a gh-token-monitor mechanism, and spreads through compromised publishing accounts. It lists IOCs (lib/setup.mjs, lib/Math_Symbol.js) and warns to remove the persistence before revoking stolen GitHub tokens, since revocation triggers a destructive routine. Socket detected the release about 11 minutes after publication.

npmTensorlakeSocket+3
Shai-HuludChainDropgh-token-monitor+2

Supply Chain, Threat IntelΒ· Added 11 Oct 2026, published 9 Oct 2026

arxiv.orgpaper🧠 AI

AgentTune: A Unified Training Lifecycle for Tool-Using LLM Agents

AgentTune is a source-available Python library that unifies building, training, evaluating, distilling and maintaining tool-using LLM agents. Its core is a two-tier EventLog representation that preserves agent trajectories and yields consistent projections for training, evaluation and auditing. On top of it sit a shared agent runtime, tool-calling reinforcement learning, agentic distillation, RAG, decision workflows, evaluation utilities and a designed path toward self-healing agents, demonstrated on tasks such as legal contract search.

PythonRAG
AgentTune

agents, training, researchΒ· Added 12 Oct 2026, published 9 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

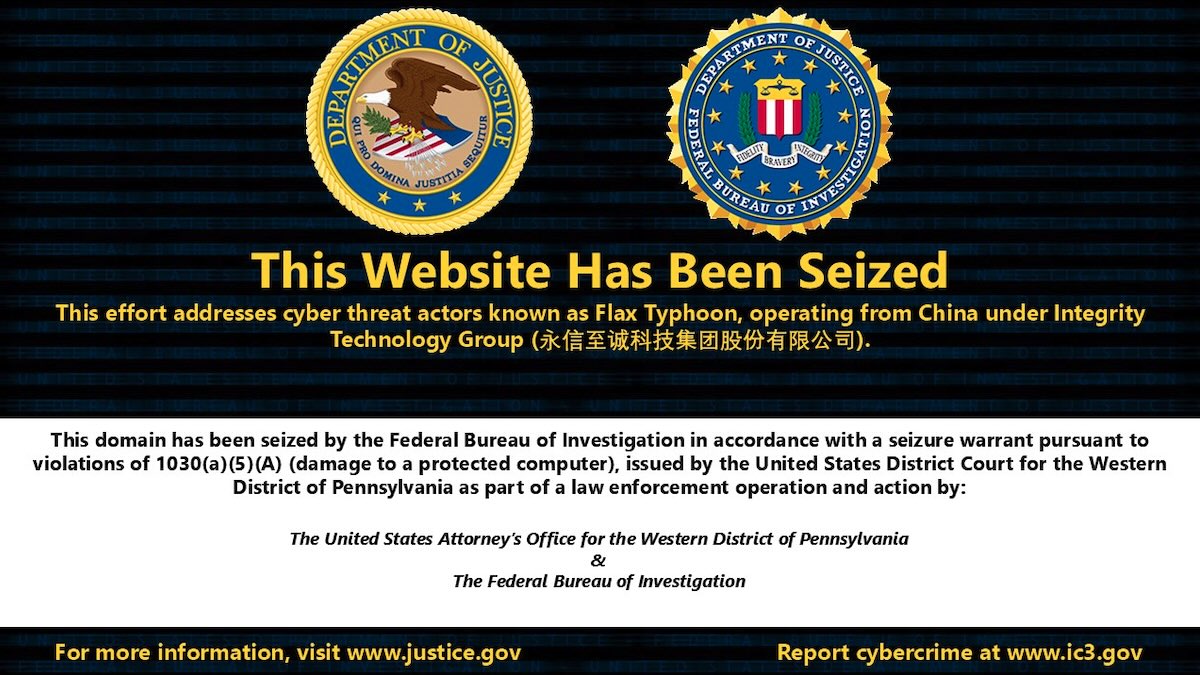
US Disrupts Chinese State-Sponsored Hacking Tools

The US, alongside UK, Australian, Canadian, Japanese, New Zealand, and Spanish agencies, disrupted MicroScan and FishHub, hacking tools built by China's Integrity Technology Group and used by the state-sponsored actor Flax Typhoon (aka Ethereal Panda, Red Juliett, Storm-0919, UNC5007) against US, Japanese, Polish, and Taiwanese critical infrastructure and universities. MicroScan is a Python-based scanner with over 1,300 penetration-testing scripts targeting Apache Struts, Jenkins, WebLogic Server, WordPress, OpenSSL, and other services, delivered via a Mirai-derived IoT botnet; FishHub let operators remotely search and exfiltrate files from victim networks. The advisory also details the group's broader toolkit (SoftEther VPN for persistence, EBurst for Exchange password spraying, DC.ex for Active Directory data extraction) and the seizure of the domains used to access the tools.

NmapWordPressActive Directory+3
Flax Typhoon (Ethereal Panda, Red Juliett, Storm-0919, UNC5007)Integrity Technology GroupMicroScan+4

Threat Intel, Offensive SecurityΒ· Published and added 9 Oct 2026

opensourcemalware.comtalkπŸ›‘οΈ Security

The OpenSourceMalware Show #24

Weekly OpenSourceMalware podcast episode discussing three fresh supply-chain attacks: the Tensorlake AI-agent SDK compromised via a preinstall-triggered Mini Shai-Hulud-derived worm (setup.mjs + math_symbol.js, run via Bun) that steals credentials; a Contagious Interview-style attack where a cloned GitHub repo drops a malicious .npmrc pointing npm install at a Chinese mirror (npmmirror.com) to resolve a hidden package; and 42 malicious RubyGems published by "Ghost Dev" that typosquat/brandjack crypto tooling, sleep 20–40 minutes via extconf.rb to evade detection, then either open a reverse shell or deploy a Python-based "Wallet Guard" crypto-theft kit targeting TronLink, MetaMask, Phantom, Binance, Coinbase, Trust Wallet, Exodus, and Electrum. The hosts also discuss multi-package "combined payload" evasion and how AI-driven slopsquatting is making cross-ecosystem typosquats more effective.

npmRubyGemsBun+2
Mini Shai-HuludContagious InterviewDPRK+16

Supply Chain, Malware & REΒ· Published and added 9 Oct 2026

adversa.aiarticleπŸ›‘οΈ Security

Top MCP security resources β€” October 2026

Adversa AI's October 2026 MCP security roundup, aggregating and synthesizing 15 resources: authentication-bypass vulnerabilities in LiteLLM's MCP endpoint (CVE-2026-59822, now CISA KEV), Grafana's MCP server session spoofing/SSRF (CVE-2026-19516), an MCP Python SDK OAuth-fallback flaw exploited by a malicious server returning a 404, and an Obot gateway route-matching bypass reopening GHSA-vw82. It also covers detection failures (two malicious MCP servers passing five scanners including Cisco mcp-scanner and Snyk agent-scan, 12% of 82,000 public MCP configs hardcoding secrets), a malicious npm wallet-signing package (gadgethumans-mcp), the A2M agent-hijacking attack technique, and CoSAI's MCP Security v2.0 governance model.

Model Context ProtocolLiteLLMnpm+3
CVE-2026-59822CVE-2026-59821CVE-2026-19516+6

AI Security, AppSec, Identity & AccessΒ· Published and added 8 Oct 2026

github.comrepoπŸ›‘οΈ Security

target/strelka

Strelka is Target's open-source, container-based real-time file scanning system for threat hunting, threat detection, and incident response, built in Go and Python. It runs 50+ scanners (YARA, PE parsing, encrypted ZIP cracking, entropy analysis, etc.) to extract metadata and content from files at enterprise scale, which can feed a SIEM for alerting on suspicious artifacts like an Emotet-laden encrypted ZIP payload.

DockerGoPython+1
Laika BOSSEmotet

Blue Team & DetectionΒ· Added 8 Oct 2026

github.comrepo🧠 AI

Tracer-Cloud/opensre

OpenSRE is an open-source framework for building AI SRE agents that resolve production incidents by correlating logs, metrics, traces, deploys and runbooks across 60+ connected tools (observability, cloud infra, incident management, MCP). Beyond the agent runtime (CLI, Python API, Slack/PagerDuty/Telegram integrations), the project's stated mission is to build an RL training and evaluation environment β€” explicitly modeled on SWE-bench's role for coding agents β€” to scale realistic infrastructure-failure scenarios as a benchmark for AI SRE.

DockerPythonPostgreSQL+3
OpenSRETracer-CloudSWE-bench

agents, evals, ai-infraΒ· Added 8 Oct 2026

xda-developers.comarticle🧠 AI

I'm not paying $20 for ChatGPT or Claude because a free local LLM does

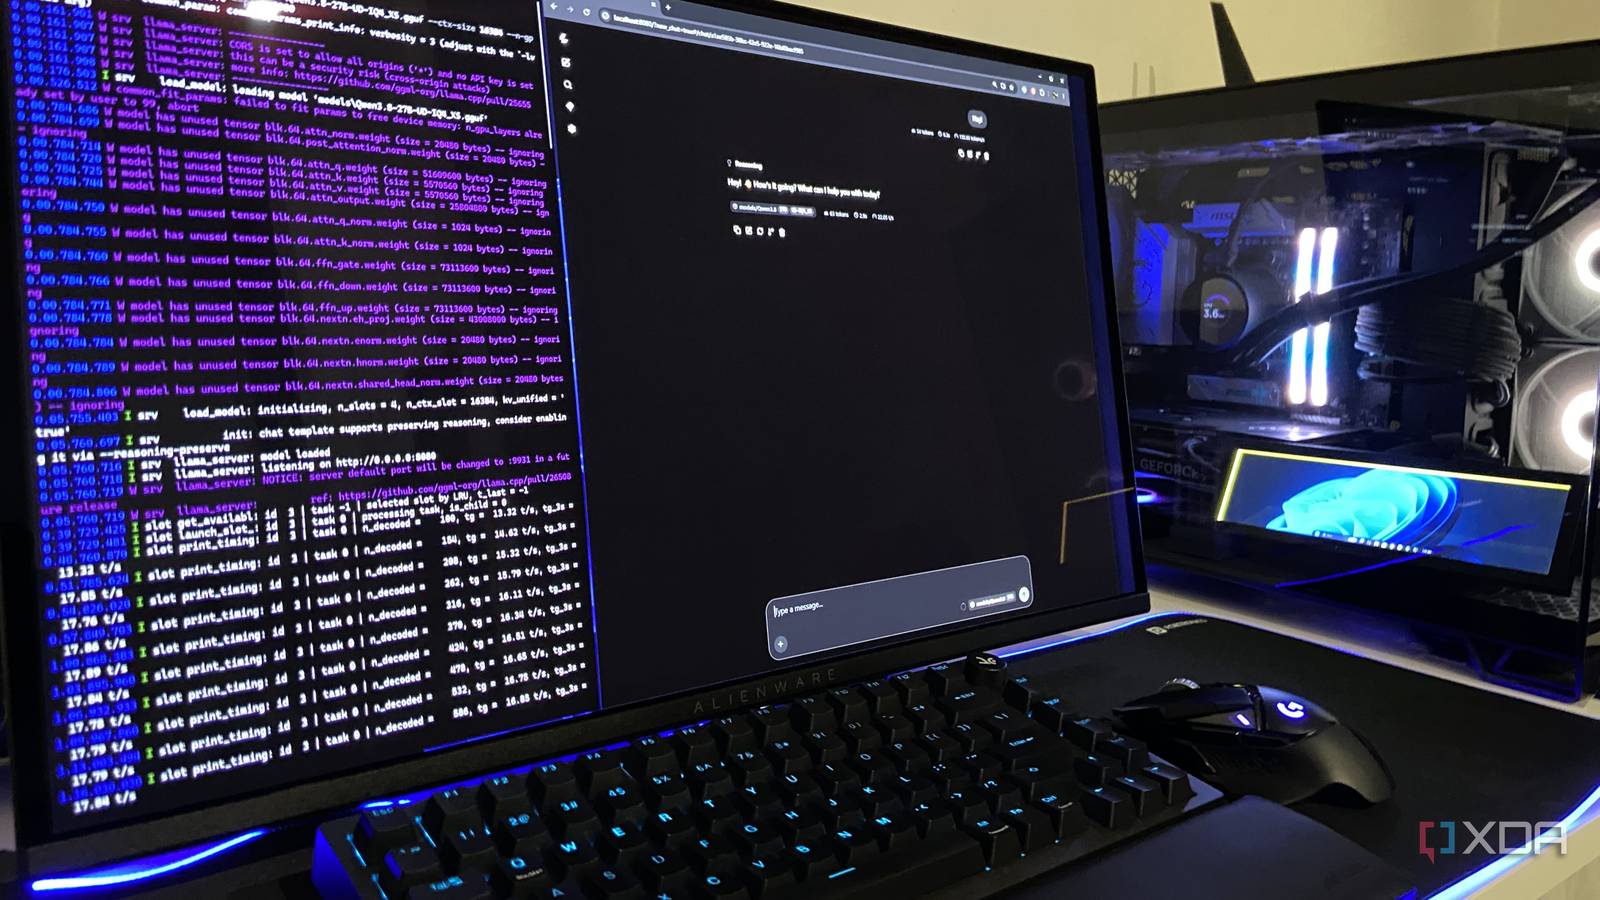
A personal workflow writeup describing how the author replaced $20 per month ChatGPT and Claude subscriptions with Qwen3.8-27B (Unsloth UD-IQ4_XS GGUF quant, 13.3GB) run locally via llama.cpp on a 4070 Ti Super GPU with 16GB VRAM, achieving about 33.7 tokens per second at a 16K context window. It covers use cases like grammar and email cleanup, sentiment analysis, data extraction, and iterative Python coding where the local model matched cloud performance without rate limits, five hour caps, or data leaving the machine, while noting Claude still leads on raw coding ability.

llama.cppQwen3.8-27BGGUF+3
UnslothChatGPTClaude+1

inference, modelsΒ· Added 8 Oct 2026, published 7 Oct 2026

arxiv.orgpaperπŸ›‘οΈ Security

Applying Security by Design at the Point of Execution: How Governed Security Requirements Affect the Security of AI-Generated Code

Evaluates delivering security requirements from a governed security-by-design knowledge base (SbD-ToE) to a code-generating LLM through an MCP server at generation time. On DualGauge (59 Python tasks) the share passing all security tests rose from 44.1% to 78.0%; on BaxBench (28 backend scenarios) the share of functionally correct solutions with no successful exploit rose from 65% to 86%, matching the authors' Oracle Security Reminder (85%). The joint secure-and-functional metric did not improve significantly, since stricter code failed functional tests that fix unstated values. The study used one model and one generation per task, and it proposes measuring conformance with applicable requirements rather than only detecting known weaknesses.

Model Context ProtocolLLMPython
SbD-ToEDualGaugeBaxBench+2

AI Security, AppSecΒ· Added 9 Oct 2026, published 7 Oct 2026

arxiv.orgpaper🧠 AI

Applying Security by Design at the Point of Execution: How Governed Security Requirements Affect the Security of AI-Generated Code

The preprint tests whether security requirements from a governed security-by-design knowledge base (SbD-ToE), delivered to a code generator through a Model Context Protocol server at generation time, make AI-written code more secure. On DualGauge (59 Python tasks, LLM-judge scoring) the share of tasks passing all security tests rose from 44.1% to 78.0%. On BaxBench (28 backend scenarios with real exploits in containers) the share of functionally correct solutions with no successful exploit rose from 65% to 86%, comparable to the authors' Oracle Security Reminder (85%). The pre-specified joint secure-and-functional metric did not improve significantly, and the stricter code failed functional tests that fix values the task never states. The study used one model and one generation per task. The authors argue that current benchmarks only detect the weaknesses their evaluators were built for, and propose measuring conformance with the requirements that apply.

Model Context ProtocolPython
DualGaugeBaxBenchSbD-ToE+1

evals, mcp, coding-agentsΒ· Added 9 Oct 2026, published 7 Oct 2026

rapid7.comwriteupπŸ›‘οΈ Security

CVE-2026-21589: Critical unauthenticated arbitrary file access in Atlassian products

Rapid7's analysis of CVE-2026-21589 (CVSSv4 9.3), a critical unauthenticated arbitrary file read vulnerability affecting Bitbucket, Confluence, Jira Software/Service Management, Bamboo, Crowd, Crucible, and Fisheye Data Center products. It summarizes watchTowr Labs' root-cause finding that double-colon (::) sequences can act as path separators in Atlassian's web-resource handling, enabling path traversal to read arbitrary files within the Tomcat web root β€” including crowd.properties credentials that can be chained to create a rogue jira-administrators account. The post provides emergency patching guidance, Atlassian's WAF/RewriteValve mitigations, log-hunting regex, and notes public Python PoC and Nuclei templates exist.

BitbucketConfluenceJira+3
CVE-2026-21589CWE-552watchTowr Labs+1

AppSecΒ· Published and added 7 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

Analysis of CVE-2026-105844, a CWE-1321 prototype-pollution vulnerability in @payloadcms/plugin-import-export that the vendor says can lead to unauthenticated remote code execution. It covers affected ranges (stable 3.0.0–3.87.x, canary 4.0.0-canary.0–canary.26), the fix (3.88.0 / 4.0.0-canary.27), the patched field-path guard against __proto__/constructor/prototype segments, and a six-step SOC hunting/triage playbook with two offline Python scripts for inspecting npm package trees and triaging request field-paths for prototype-sensitive values.

Payload CMSnpmCVSS+3
CVE-2026-105844CWE-1321GHSA-qf28-8hc6-vwrp+1

AppSec, Blue Team & DetectionΒ· Added 8 Oct 2026, published 7 Oct 2026

devopscube.comwriteup🧠 AI

Kubernetes Agent Sandbox on AWS EKS (Step-by-Step Guide)

Kubernetes Agent Sandbox on AWS EKS is a step-by-step tutorial for the kubernetes-sigs agent-sandbox controller with gVisor. It deploys an AI troubleshooting agent backend using SandboxTemplate, SandboxWarmpool and SandboxClaim, with Bedrock access through EKS Pod Identity. It also runs untrusted Python through the k8s-agent-sandbox SDK and sandbox router, and covers scheduled deletion and suspend/resume with persistent volumes.

KubernetesAWSAmazon EKS+9

agents, ai-infraΒ· Added 21 Oct 2026, published 7 Oct 2026

devopscube.comwriteupπŸ›‘οΈ Security

Kubernetes Agent Sandbox on AWS EKS (Step-by-Step Guide)

Tutorial on setting up Kubernetes Agent Sandbox (kubernetes-sigs/agent-sandbox) with gVisor on an AWS EKS cluster. It runs a troubleshooting AI agent backend inside a sandbox using SandboxTemplate, SandboxWarmpool and SandboxClaim, and runs untrusted Python through the k8s-agent-sandbox SDK and Sandbox Router. Probes show blocked /etc/shadow reads, setuid and service account token access, plus host process isolation. It also covers scheduled deletion and suspend/resume with persistent volumes.

KubernetesgVisorAWS+3
sandbox escapeSandboxTemplateSandboxWarmpool+3

AI Security, Cloud & Infra, LearningΒ· Added 21 Oct 2026, published 7 Oct 2026

github.comrepo🧠 AI

Show HN: NanoMuse – An open-source AI agent for your phone and computer

nanoMuse is an open-source personal AI agent that runs across phone, desktop, and web, built on an on-device sandbox (OpenMinis with proot/Alpine Linux on mobile) and the DeepSeek Harness on desktop with a Python runtime for tool use. Devices share one account and sync conversations through a relay (self-hostable), while the agent proactively acts, retains memory, and pauses before irreversible actions; it is released GPL-3.0-or-later with documentation on install, self-hosting, connectors, and memory.

Model Context ProtocolPythonDeepSeek+2
nanoMuseMetaDeepSeek Harness+13

agentsΒ· Published and added 7 Oct 2026

vulnerablemcp.inforepoπŸ›‘οΈ Security

The Vulnerable MCP Project β€” MCP vulnerability database

The Vulnerable MCP Project is a curated, continuously growing database of security vulnerabilities and attack techniques specific to the Model Context Protocol ecosystem. Entries cover concrete CVEs (e.g. CVE-2025-68143/68144/68145 in Anthropic's mcp-server-git), transport-layer SDK flaws (cross-client response leakage, missing DNS rebinding protection in the official TypeScript/Python SDKs), unauthenticated/0.0.0.0-bound servers enabling RCE (MCPJam inspector, MCP Inspector, Grafana MCP), command/path injection in dozens of third-party servers (gemini-mcp-tool, mcp-server-kubernetes, Framelink Figma MCP, Zen MCP, filesystem-mcp), SSRF chains reaching cloud metadata (MarkItDown MCP, mcp-fetch-server), and a large set of AI-specific attacks: tool poisoning, trigger-phrase data exfiltration, prompt injection via GitHub issues, Jira and Google Docs, rug-pull tool mutation, and cross-server tool-name collisions. It functions as the de facto vulnerability registry for the MCP ecosystem, useful for tracking disclosed issues before patching or adopting third-party MCP servers.

Model Context ProtocolCursorKubernetes+3
CVE-2025-68143CVE-2025-68144CVE-2025-68145+3

AI Security, AppSecΒ· Added 6 Oct 2026

github.comrepo🧠 AI

Microsoft Agent Framework python-1.20.0 release

Release notes for python-1.20.0 of Microsoft's Agent Framework, an open-source agent/workflow orchestration library. This release adds native vector-store connectors for DuckDB, SQL Server and MongoDB plus a TypeSafe AI connector, redesigns Foundry hosting around request-scoped agent factories and sandbox-isolated sessions, adds computer-use support to Responses clients, and ships Magentic manager and handoff-routing improvements for multi-agent orchestrations alongside a large batch of MCP, Bedrock, Gemini, Anthropic and Ollama provider fixes.

Model Context ProtocolPythonDocker+7
MicrosoftMicrosoft Agent FrameworkDuckDB+4

agentsΒ· Added 6 Oct 2026

theravenfile.comwriteupπŸ›‘οΈ Security

CITRIX 0-DAY EXPLOITS: CVE-2026–88771 & CVE-2026–88772 IN THEΒ WILD

An incident-response style deep dive into active in-the-wild exploitation of Citrix NetScaler ADC/Gateway via CVE-2026-88771 (unauthenticated RCE through log-poisoning of ns_monuploadd_err.pl) and CVE-2026-88772 (DTLS memory overflow), part of 8 CVEs disclosed by Citrix on September 27, 2026. The author reverse-engineers the full post-exploitation toolkit dropped after root is obtained: SLAPSHOT (a Perl/Python loopback TCP tunneler/pivot), WHIPSHOT (a disguised PHP web shell served via fake CSS paths), the Platypus C2 agent, and a Perl "Pitboss" dropper script (with full decoded source and an embedded SHA-256-protected PHP web shell) that creates a rogue superuser, SUIDs /bin/sh, exfiltrates NetScaler config, and patches httpd.conf for persistence. It closes with extensive IOCs (C2 IPs, file hashes, paths, credentials) and patch guidance for affected NetScaler builds.

Citrix NetScalerPHPPython+2
CVE-2026-88771CVE-2026-88772CVE-2026-88773+10

Threat Intel, Malware & REΒ· Published and added 6 Oct 2026

x.comwriteupπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge CVE-of-the-Day #070 on CVE-2026-61500 in Rejetto HFS 3.0.0–3.2.0. The default Koa session-signing key came from Math.random() (CWE-338) and the unauthenticated login handshake leaked outputs of the same generator. That allows recovery of the key, a forged administrator session, and code execution through the legitimate server_code feature. It covers scoring (CVSS 9.8/9.3, EPSS, KEV status), the 3.2.1 fix, a six-step SOC hunting and remediation trail (loginSrp1/2, get_config/set_config pivots, COOKIE_SIGN_KEYS review), and offline jq/Python helpers for container and config metadata.

Rejetto HFSKoaDocker+2
CVE-2026-61500CWE-338VulnCheck+6

Blue Team & Detection, AppSec, Identity & AccessΒ· Added 9 Oct 2026, published 6 Oct 2026

securitylabs.datadoghq.comwriteupπŸ›‘οΈ Security

Beyond valid credentials: How exposed AWS keys are tested for Amazon Bedrock access

Datadog Security Labs describes how attackers test stolen AWS credentials for Amazon Bedrock access. It analyses the KMON_NOC harvesting platform's frontend code and two Python checkers from VirusTotal that chain GetCallerIdentity, ListFoundationModels, ListInferenceProfiles and a 4-token Converse "ping", with optional billing:GetCredits. Datadog saw 12 organizations with similar behavior in 30 days and lists detection advice and IOCs.

AWS BedrockAWSAWS IAM+3
KMON_NOCLLMjackingcredential validation+8

Cloud & Infra, Threat Intel, Blue Team & DetectionΒ· Added 29 Oct 2026, published 6 Oct 2026

x.comthreadπŸ›‘οΈ Security

Ayyaz (@ayyazdev) on X

A security researcher's thread breaks down CVE-2026-105135, an unpatched critical (CVSS 10.0) remote code execution vulnerability in InternLM's MindSearch agent with a public PoC. The flaw is in ExecutionAction.run in mindsearch/agent/graph.py, which passes the planner LLM's output directly to Python's exec() β€” if the model's reply lacks a code fence, the entire response is executed, and a crafted query to the /solve endpoint can get the model to emit attacker-controlled code that runs as root inside the shipped Docker container (which binds 0.0.0.0:8002). The author notes prompt filtering cannot fix this since the attacker only needs the model's output to contain code, and recommends running any agent that executes model-written code in a network-isolated, non-root sandbox kept off public ports.

PythonDockerCVSS+1
CVE-2026-105135VulDBInternLM

AI Security, AppSecΒ· Added 7 Oct 2026, published 5 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

HyBind: Structural Analysis of PQ/T Hybrid Cryptographic Usage

HyBind is an intraprocedural Python static-analysis framework that traces cryptographic component secrets through code to determine whether post-quantum/traditional (PQ/T) hybrid key-derivation and signature-verification logic actually requires both algorithms to succeed, rather than silently accepting a result from only one. It uses registered API contracts and function-return/execution-effect checks to distinguish real AND-logic hybrids from presence-based heuristics that wrongly treat joint and single-algorithm contributions as equivalent. The authors validate it on 50 controlled fixtures and 33 programs (15 using native ML-KEM/X25519 and ML-DSA/Ed25519 APIs), showing relaxed checks can misclassify traditional-only results as hybrid.

Python
ML-KEMX25519ML-DSA+1

AppSecΒ· Added 8 Oct 2026, published 5 Oct 2026

dfir.chwriteupπŸ›‘οΈ Security

Today I learned: Python's .start Files as a Persistence Mechanism

Explains PEP 829's new .start files in Python 3.15, which let a package register package.module:callable entries in site-packages that execute automatically every time an interpreter starts, before any user code runs. The author walks through a reproducible lab showing code execution via a .start file, contrasts it with the older executable-import .pth file technique it replaces, and gives forensic hunting commands (using python -S to avoid triggering the mechanism during investigation) to locate and audit .start files on disk.

Python
PEP 829

Blue Team & Detection, Offensive SecurityΒ· Added 6 Oct 2026, published 4 Oct 2026

github.comrepoπŸ›‘οΈ Security

DeepZero

DeepZero is an open-source orchestration engine that lets researchers define vulnerability-research pipelines declaratively in YAML, handling parallel execution (ThreadPoolExecutor), resumable/fault-tolerant state, and LLM-assessment stages via LiteLLM/Jinja2 prompts. It ships example processors for Ghidra headless decompilation, LOLDrivers.io hash exclusion filtering, PE header/driver metadata extraction, and batch Semgrep scanning, with a dedicated pipeline for BYOVD kernel driver vulnerability research. An extensibility model lets users plug in custom Python processors referenced by path in the YAML config.

GhidraSemgrepLiteLLM+2
BYOVDLOLDrivers

Offensive Security, Malware & RE, AI SecurityΒ· Added 3 Oct 2026

github.comrepo🧠 AI

Jakeschincariol/replica-skill

replica-skill is an MIT-licensed set of eleven Claude skills that run an app-cloning pipeline: recon, architect, design, build, backend, test, diff, entrepreneur, brand, launch and deploy. Six standard-library Python tools handle image diffing, parity scoring, review ranking, contrast checks, rebrand sweeps and store-listing lint. It installs as a Claude Code plugin or by copying folders, and states clean-room and rebranding limits.

Claude CodeClaudePython+5
Jake SchincariolAnthropic

coding-agents, promptingΒ· Added 29 Oct 2026, published 3 Oct 2026

github.comrepo🧠 AI

Show HN: Made an open-source Lego AI generator

ldraw-nova is an open-source agentic pipeline where an LLM agent (tested with models like Claude Opus 5.5 and GPT-6 Astra) takes a build prompt, reads LDraw-building instructions, and produces a plan.json describing a model's geometry. From that plan it writes a Python generator script that, when executed, outputs an LDraw (.mpd) 3D CAD source file, viewable in 3D/VR (Meta Quest 3) or exportable to Blender-editable glTF. The agent uses jev-rerank, a semantic search tool with reranking backed by TypeSafe's Jev System One model, to find suitable LEGO parts and example models, falling back to full-text search without an API key; it also uses headless rendering and collision/gap detection to self-inspect and iterate on designs.

DockerPythonBlender+2
TypeSafeJev System Onejev-rerank+13

agents, multimodalΒ· Added 3 Oct 2026, published 2 Oct 2026

github.comrepo🧠 AI

Microsoft Agent Framework β€” python-1.20.0 release

Release notes for Microsoft's Agent Framework (Python and .NET SDKs), covering versions python-1.16 through python-1.20 and dotnet-1.19 through dotnet-1.23. Changes span native vector-store connectors (MongoDB, Qdrant, PostgreSQL/pgvector, DuckDB, SQL Server, Azure Cosmos DB, Azure AI Search), Foundry hosting redesigns around request-scoped agent factories and durable Invocations, MCP skill/session security hardening (approval binding, security labels, ZIP-only skill archives), Magentic multi-agent orchestration and handoff routing, and checkpoint/replay correctness fixes across workflows.

PythonModel Context ProtocolMongoDB+10
MicrosoftTypeSafe AIMistral+1

agents, mcpΒ· Added 2 Oct 2026

huggingface.corepo🧠 AI

Kyutai Pocket TTS

Pocket TTS is a 100M-parameter text-to-speech model from Kyutai designed to run efficiently on CPU, generating audio faster than real-time (~6x on a MacBook Air M4) with ~200ms latency to first audio chunk and voice cloning from short audio samples. It supports English, French, German, Portuguese, Italian, and Spanish, ships a Python library and CLI, and has spawned numerous community ports (WASM, ONNX, Rust/Candle, MLX, C++, C#) and fine-tuned language variants (Czech, Hindi, Korean, Persian, Indonesian, Estonian, Welsh, Polish).

PyTorchPythonHugging Face+6
KyutaiManu OrsiniSimon Rouard+4

models, multimodalΒ· Added 2 Oct 2026

blog.trailofbits.comwriteupπŸ›‘οΈ Security

SequenceHash: multihashing for the rest of us

Trail of Bits introduces SequenceHash and its keyed variant SequenceMAC, hash-agnostic multihashing constructions similar in goal to NIST's TupleHash but not tied to Keccak, working with SHA256/384/512, BLAKE, and RIPEMD. The spec, now part of the Community Cryptography Specification Project, provides unambiguous input encoding, length-extension prevention, built-in customization strings, and HMAC-style keyed MACs that avoid HMAC's key-pseudocollision issues; reference implementations ship in Rust, Go, and Python with full test vectors.

RustGoPython
TupleHashHMACNIST SP 800-185+10

AppSecΒ· Published and added 2 Oct 2026

github.comtoolπŸ›‘οΈ Security

https://github.com/praetorian-inc/gato

Gato (GitHub Attack Toolkit) from Praetorian is a Python CLI for enumerating and attacking GitHub organizations' CI/CD pipelines: it identifies poisoned pipeline execution risks, abuses self-hosted runners via workflow and run-log analysis, exfiltrates Actions secrets, and automates fork-PR/workflow-based command execution. Version 1.7 added an Actions Artifacts Secrets Scanner that downloads and recursively scans workflow artifacts with NoseyParker, which Praetorian used to find critical secrets leaks in prominent open-source projects. The project is now archived/superseded by Praetorian's multi-platform tool Trajan, which merges Gato (GitHub) and Glato (GitLab) attack capabilities.

GitHub ActionsGitHubPython+2
poisoned pipeline execution

DevSecOps, Offensive SecurityΒ· Published and added 2 Oct 2026

x.comtoolπŸ›‘οΈ Security

Python Hub (@PythonHub) on X

TATS is an open-source Python tool that analyzes OAuth 2.0, OpenID Connect, and Microsoft Entra ID tokens. It helps security researchers trace authentication flows, identify risky permissions granted to tokens, and visualize token lifecycles for identity security review and investigation work.

PythonOAuthOIDC+1
TATS

Identity & AccessΒ· Published and added 2 Oct 2026

github.comrepo🧠 AI

zzzz7788990213-ops/EvoVLM

EvoVLM searches over prompts, image preprocessing, generation budgets and answer extraction for frozen Qwen3-VL-2B-Instruct and Qwen3-VL-2B-Thinking, without fine-tuning weights. A local Qwen model ranks a catalog of typed mutations, a trusted renderer produces Python programs, and Pareto selection on accuracy and latency drives two small generations on scientific chart understanding (CharXiv subset). Recorded results on Dev128: Evolved Instruct keeps accuracy with 8.9% lower median latency, and Evolved Thinking gains 16.41 points of accuracy with 10.6% lower median latency. CPU-only replay and fail-closed evidence verification are included. The authors state the limits: small sample, overlap with the evolution set, and results tied to the recorded hardware.

Qwen3-VLvision-language modelPython+3
QwenCharXivNSGA-II

research, multimodal, evalsΒ· Added 16 Oct 2026, published 2 Oct 2026

simonwillison.netarticle🧠 AI

pwasm 0.2a0

Simon Willison describes pwasm, a pure-Python WebAssembly engine he originally vibe-coded in January, and how he later let Claude Opus 5.5 work on it autonomously with minimal prompting: over 42 commits the model extended it to handle almost all of the WASM spec and got working builds of MicroPython, QuickJS and Micro QuickJS running inside it, bundled in the PyPI wheel. He frames it as a rough but telling illustration of how much more capable today's coding agents are than the models used ten months earlier, while still not trusting the alpha-tagged result.

PythonWebAssembly
Simon WillisonClaude Opus 5.5pwasm

coding-agentsΒ· Added 8 Oct 2026, published 1 Oct 2026

x.comthread🧠 AI

Samuel Zeng (@SamuelZengML) on X

Samuel Zeng announces the open-sourcing of Edge0's cross-platform app layer (iOS, macOS, Android, Windows), building on Edge0's earlier on-device 35B language model that runs in only 1-2.5GB of peak memory. The release includes app code, local model/runtime integration, model management, and build/deployment guides on GitHub; the technique keeps the full model on local storage and streams in only the experts (MoE-style) needed per step, predicting and prefetching the next experts while running storage reads in parallel with compute. A Q4 2026 roadmap promises a unified inference API across platforms plus Python, hardware-adaptive runtime, and a CUDA backend.

CUDAPythonMixture of Experts
Samuel ZengEdge0

inferenceΒ· Published and added 1 Oct 2026

arxiv.orgpaperπŸ›‘οΈ Security

AuraForge: Scaling Security Supervision for Training Coding Agents

AuraForge is a method for synthesizing and validating executable security tests to train coding agents toward secure (not just functionally correct) code, combining attack-oriented test synthesis, multi-language task construction, and safeguards against reward hacking. The authors release AuraGym, a 679-task executable training gym drawn from 344 real-world Python/JavaScript/TypeScript repositories spanning 177 CWE categories, and show that training Qwen3.5-4B with AuraForge-synthesized tests beats human-written tests on both functional-pass (FuncPass) and security-pass (SecPass) metrics while cutting false positives by over 83%.

QwenPythonJavaScript+1
AuraGymQwen3.5-4B

AI Security, AppSecΒ· Added 3 Oct 2026, published 1 Oct 2026

arxiv.orgpaper🧠 AI

AuraForge: Scaling Security Supervision for Training Coding Agents

AuraForge is a pipeline that synthesizes and validates executable security tests to supervise the training of coding agents, using attack-oriented test synthesis and safeguards against reward hacking. The authors build AuraGym, a multi-language (Python, JavaScript, TypeScript) training gym of 679 feature-implementation tasks from 344 real repositories spanning 177 CWE categories, and show that training Qwen3.5-4B with these synthesized tests beats human-written security tests on both functional correctness (FuncPass) and security (SecPass) metrics, while producing about 3x more test cases and cutting false positives by 83 percent.

Qwen3.5PythonJavaScript+1
AuraForgeAuraGymQwen3.5-4B

research, training, coding-agentsΒ· Added 2 Oct 2026, published 1 Oct 2026

github.comrepo🧠 AI

feder-cr/invisible_playwright_mcp

invisible_playwright_mcp is an MCP server (and companion Python library, invisible_playwright) that wraps Playwright so an LLM agent can operate a real browser like a human: clicking, typing, scrolling and reading page content, useful for tasks like checking flight fares across a date range where no API exists. It ships a standalone chat+live-browser UI driven by any OpenRouter model, installs as a plugin for Claude Code, Codex and Gemini CLI, and exposes stealth/identity controls (seed-based browser fingerprint, proxy-derived timezone/locale/geolocation, persistent profile directories) via its invisible_core component.

Model Context ProtocolPlaywrightPython+4
GitHub

mcp, agentsΒ· Added 7 Oct 2026, published 29 Sep 2026

github.comrepoπŸ›‘οΈ Security

garak v0.17.0 β€” LLM vulnerability scanner release

Release notes for garak v0.17.0, NVIDIA's open-source LLM vulnerability scanner used for red-teaming and probing models for jailbreaks, prompt injection, data leakage and other failure modes. The release adds an EU AI Act risk-category mapping to tag and group probe results, plus fixes to detectors (agent_breaker judge verdict validation, packagehallucination import parsing, MarkdownExfilContent divide-by-zero, TriggerListDetector alignment) and probes (badchars ASCII selection, Markdown exfiltration link templates), along with Ollama generator improvements and dropped Python 3.10 support in favor of 3.13.

OllamaPython
EU AI ActAgentBreakerIntentProbe+2

AI SecurityΒ· Added 29 Sep 2026

wiz.iowriteupπŸ›‘οΈ Security

The Blue Agent POV: Investigating Multi-Platform Data Exfiltration Across AWS and GitHub

Wiz walks through a case study of its "Blue Agent" autonomous SOC investigator tracing a compromised CI/CD service account (svc_automation) across AWS and GitHub. The attack chain: a stolen GitHub token cloned 18 private repos containing hardcoded AWS keys, which were used to authenticate to AWS from Kali Linux via a Zenlayer VPN IP, pivot to a second account, run SSM SendCommand against a production Windows domain controller, and stage custom Python exfiltration scripts (mssql_table_export.py, pg_table_export.py, billing_export2.py) in S3 to pull data from MSSQL, PostgreSQL, and billing systems. The piece details the investigative technique used - 30-day baseline comparison, ASO/IP dispersion across the tenant, and correlating CloudTrail management-plane events with S3 data-plane events and GitHub audit logs.

AWSGitHubKali Linux+3
AWS IAMSSM SendCommandAssumeRole

Blue Team & Detection, Cloud & InfraΒ· Published and added 29 Sep 2026

blog.modelcontextprotocol.ioarticle🧠 AI

The Official Ruby SDK for MCP Reaches Tier 1

The official Ruby SDK for the Model Context Protocol (the mcp gem) became the sixth Tier 1 MCP SDK in September 2026, after TypeScript, Python, C#, Go and Rust. Version 1.2.0 supports the 2026-07-28 spec revision, including the stateless lifecycle, multi round-trip requests and cache hints. The SDK passes 67/67 server and 50/50 client conformance runs, and the post gives install and upgrade steps.

Model Context ProtocolRubymcp gem+6
Topher BullockKoichi ItoAteş Gâral+4

mcpΒ· Added 30 Oct 2026, published 29 Sep 2026

github.comrepo🧠 AI

dagoSte/squadra

Squadra (version 3.11.0) is an MIT-licensed Python 3.12+ tool that coordinates several Claude Code, Codex and interactive Cursor windows on one project through a shared local registry. It records tasks, acknowledgements, source-bound proofs and independent reviews by a window that did not write the code. A local dashboard shows progress, per-window token usage and model-balance suggestions, and community plugins extend it. The page was truncated, so later sections are not covered.

Claude CodeCodexCursor+6
SquadraSentrymemoranda

agents, coding-agentsΒ· Added 27 Oct 2026, published 28 Sep 2026

github.comrepoπŸ›‘οΈ Security

SpecterOps/Blacklight β€” local AI agent attack surface mapping toolkit

Blacklight is a SpecterOps toolkit for endpoint forensics on AI coding agents, split into Scout (bounded metadata/filesystem triage across Codex, Claude Code, Cursor, Antigravity CLI, and Grok that finds candidate session artifacts without reading their contents) and Session Analysis (a Python CLI that parses selected JSONL/SQLite session downloads from Codex, Claude Code, Cursor, and Antigravity CLI into ranked, redacted local reports). It's built for investigators who need to identify and review AI agent session history on a host β€” surfacing config, auth metadata, and high-value indicators β€” while explicitly leaving secret scanning to external tooling; paths are informed by SpecterOps' Endpoint AI Agent Abuse (EAA) technique catalog.

Claude CodeCodexCursor+3
Endpoint AI Agent Abuse (EAA) technique catalog

Blue Team & Detection, AI SecurityΒ· Added 27 Sep 2026

github.comotherπŸ›‘οΈ Security

MCP Python SDK v2.2.0

Release notes for MCP Python SDK v2.2.0 detailing several security-relevant default changes: HTTP clients (Client, streamable_http_client, sse_client) now only follow redirects within the same origin, closing a cross-origin redirect trust gap; OAuth clients now validate the authorization server's issuer even on the legacy (non-protected-resource-metadata) discovery path, preventing metadata/issuer mismatch attacks; idle Streamable HTTP sessions now expire after 30 minutes with a 10,000-session cap to limit resource exhaustion; and a new AuthSettings.validate_token_resource setting lets servers reject bearer tokens not issued for them (audience/resource confusion). Deprecation warnings push OAuth provider configs toward requiring an explicit issuer ahead of a 3.0 breaking change.

Model Context ProtocolPythonOAuth
MCPDeprecationWarning

Identity & Access, AppSec, AI SecurityΒ· Added 27 Sep 2026

github.comrepoπŸ›‘οΈ Security

garak v0.17.0 β€” adds EU AI Act risk-category mapping

garak is NVIDIA's open-source LLM vulnerability scanner that runs probes/detectors for jailbreaks, prompt injection, PII leakage, package hallucination, markdown exfiltration and more against LLM targets. This v0.17.0 release adds a new EU AI Act risk-category mapping to tag and group probe results by the Act's risk categories, alongside fixes to the agent_breaker judge, markdown-exfiltration detectors, Ollama auth/generation support, and dropped Python 3.10 in favor of 3.13 support.

garakOllamaAWS Bedrock+2
EU AI Act

AI SecurityΒ· Added 26 Sep 2026

github.comrepoπŸ›‘οΈ Security

Agent Threat Rules (ATR) β€” open detection-rule standard for AI agent threats

Agent Threat Rules (ATR) is an open, versioned YAML rule format (ATR-YYYY-NNNNN scheme) for detecting AI-agent runtime threats β€” prompt injection, tool-poisoning, malicious SKILL.md content, and MCP exchange abuse β€” evaluated by a reference TypeScript engine (with a Python wrapper) shipped as an npm/pip package, CLI, GitHub Action, and Docker scanner with SARIF output. The project positions itself as "Sigma for agent threats," maps rules to OWASP Agentic/LLM Top 10, MITRE ATLAS, and NIST AI RMF, and publishes an extensive (and unusually self-critical) benchmark suite against corpora like garak, PromptBench, and PromptInject, including documented harness bugs and withdrawn recall figures.

Model Context ProtocolnpmTypeScript+3
CVE-2026-26030CVE-2026-25592OWASP Top 10 for Agentic Applications+2

AI SecurityΒ· Added 26 Sep 2026

github.comrepoπŸ›‘οΈ Security

graygnatconsole/mcp-audit-tool

mcp-audit-tool is a dependency-light Python CLI that statically scans Claude Desktop, Cursor, Windsurf, Cline, Zed, and VS Code MCP configuration files for security issues, including hardcoded secrets, unpinned/rug-pull packages, pipe-to-shell installers, tool-poisoning via hidden instructions in tool descriptions, filesystem servers rooted at '/', and unauthenticated plaintext HTTP MCP endpoints. It auto-discovers configs across macOS/Linux/Windows, produces a security score/grade plus SARIF 2.1.0 output for GitHub Code Scanning, and is built around the OWASP MCP Top 10 categories with a CI/CD example that fails builds on severity thresholds. The roadmap adds live server probing over stdio/SSE for runtime rug-pull detection and an ML-based prompt-injection classifier for tool descriptions.

Model Context ProtocolClaude DesktopCursor+7
OWASP MCP Top 10

AI Security, DevSecOpsΒ· Published and added 26 Sep 2026

agentthreatrule.orgotherπŸ›‘οΈ Security

Agent Threat Rules (ATR) β€” Sigma/YARA-style open detection format for AI agent threats

Agent Threat Rules (ATR) is an open, versioned YAML rule format for detecting AI-agent security threats β€” prompt injection, tool poisoning, credential exfiltration, unauthenticated agent execution β€” positioned as "what Sigma is to SIEM and YARA is to malware." Rules carry permanent ATR-YYYY-NNNNN IDs, declare detection conditions against fields like LLM I/O, tool-call args, or SKILL.md content, and map back to OWASP Agentic/LLM Top 10, MITRE ATLAS, SAFE-MCP, and NIST AI RMF; a reference TypeScript engine and Python wrapper ship MIT-licensed. Governance is transitioning from a single BDFL maintainer to a Technical Steering Committee, and the spec is notably transparent about its own limits, withdrawing previously published per-lane false-positive figures after discovering a tainted benign corpus.

SigmaYARAMITRE ATLAS+3
OWASP Top 10 for LLM ApplicationsOWASP Top 10 for Agentic ApplicationsNIST AI RMF+2

AI Security, Blue Team & DetectionΒ· Added 26 Sep 2026

github.comrepoπŸ›‘οΈ Security

Sandyaa β€” open-source autonomous code auditor that proves bugs with working exploit PoCs

Sandyaa is an open-source autonomous code-audit tool that points at a local directory or git URL and runs end-to-end, driven by the Claude Code CLI (optionally Gemini) with no separate API key required. It uses a Recursive Language Model approach β€” the model drives a Python REPL to chunk code, spawn sub-LLM queries, and aggregate results β€” running eight recursive passes (call-chain tracing, data-flow expansion, vulnerability chaining, exploitability proof, etc.) and an attacker-control-reachability analyzer to filter unreachable findings, then writes each finding with a working exploit PoC and an evidence.json linking claims to file/line. Maintained by SecureLayer7, who report using it to surface zero-days; it's alpha-stage, macOS-tested, Linux/WSL2-expected-to-work, and unsupported on native Windows.

Claude CodeGeminiNode.js+2
SecureLayer7

AppSec, AI SecurityΒ· Added 26 Sep 2026

github.comrepo🧠 AI

MCP Python SDK v2.2.0

Release notes for MCP Python SDK v2.2.0, the reference Python implementation of the Model Context Protocol. Key changes: HTTP client redirects are now restricted to the same origin as the endpoint, idle Streamable HTTP sessions expire after 30 minutes (with a 10,000-session cap), OAuth authorization server metadata issuer checks are now enforced on the legacy discovery path, and new deprecation warnings push toward requiring explicit `issuer=` and `validate_token_resource` settings ahead of a 3.0 release.

Model Context ProtocolPython

mcpΒ· Added 26 Sep 2026

github.comrepo🧠 AI

Hindsight β€” Agent Memory That Learns

Hindsight is an open-source agent memory system (MIT-licensed, self-hostable via Docker/Helm or usable as Hindsight Cloud) that goes beyond RAG-style recall by having agents learn through consolidated observations and mental models built from retained facts and experiences. It exposes retain/recall/reflect operations, a built-in MCP server per memory bank, Python/Node/Go/CLI clients, an LLM-wrapper for drop-in memory on OpenAI/Anthropic calls, and reports state-of-the-art results on the LongMemEval long-term memory benchmark, independently reproduced by Virginia Tech's Sanghani Center and The Washington Post.

Model Context ProtocolClaude CodeCodex+8
HindsightVectorize.ioLongMemEval+2

agents, mcpΒ· Added 26 Sep 2026

thehackernews.comarticleπŸ›‘οΈ Security

AWS, Google, and Vercel Agent Flaws Let Attackers Trigger Tools Without Running the Model

The Hacker News details "CoreBreak," a pattern presented at Black Hat USA 2026 by Stealth researchers Hedi Ingber and Aviyam Ivgi, in which agent harnesses from AWS, Google, and Vercel dispatched tool calls without verifying they came from an actual model turn. AWS's Bedrock AgentCore InvokeHarness API (CVE-2026-18830, CVSS 8.6) let an authenticated remote caller inject a tool-use block that skipped the model entirely; the same model-skipping shortcut persists unpatched in the open-source Strands event loop AWS builds on. Google's ADK for Python (CVE-2026-18236, CVSS 9.3, fixed in 2.5.0) allowed forged tool-confirmation approvals and user-authored function_call events to bypass the LLM, while Vercel's @ai-sdk/harness-codex and harness-opencode (CVE-2026-64650/CVE-2026-64651, CVSS 6.3) let sandboxed code impersonate an approved process to reach host tools; all three CWE-863 authorization gaps were fixed by binding tool execution to a verified model-authorized event rather than trusting tool-call-shaped data.

AWS BedrockGoogle ADKVercel AI SDK+3
CVE-2026-18830CVE-2026-18236CVE-2026-64650+9

AI SecurityΒ· Added 26 Sep 2026

nvd.nist.govadvisoryπŸ›‘οΈ Security

CVE-2026-52869: The MCP Python SDK, called mcp on PyPI, is a Python implementation of the Model Context Protocol (MCP)

CVE-2026-52869 describes a session-hijacking flaw in the MCP Python SDK (PyPI package mcp) prior to version 1.27.2: the SSE and stateful Streamable HTTP transports (mcp.server.sse.SseServerTransport and mcp.server.streamable_http_manager.StreamableHTTPSessionManager) route requests to existing sessions using only the session_id query parameter or Mcp-Session-Id header, without checking that the requesting principal matches the session's original authenticated bearer-token client. This lets a different authenticated client that learns or guesses a valid session ID inject JSON-RPC messages into another user's MCP session. CVSS 3.1 base score 7.1 (High); fixed in mcp 1.27.2.

Model Context ProtocolPython
CVE-2026-52869

AppSecΒ· Added 26 Sep 2026

github.comrepoπŸ›‘οΈ Security

rewanthtammana/Who-Let-The-Agents-Act

who-let-the-agents-act is a self-hostable lab suite (Docker/Python, Groq-backed LLM agent) with nine isolated scenarios β€” overpowered data tools, IDOR-style cross-account access, unsafe agent handoffs, refund-limit bypass, indirect prompt injection via poisoned invoices, multi-tenant RAG leakage, secret leakage through debugging, fail-open approval outages, and a multi-hop confused-deputy agent chain. Each scenario runs in multiple modes (vulnerable vs. application-enforced) against the same prompt, recording model plan, policy decision, tool calls, and DB access as JSON so a reader can directly compare what changes when authorization is enforced outside the system prompt.

PythonDocker
IDOR

AI Security, AppSecΒ· Added 26 Sep 2026

github.comrepoπŸ›‘οΈ Security

Chocapikk/CVE-2026-21858

A GitHub PoC chaining two n8n CVEs into unauthenticated RCE: CVE-2026-21858 abuses a Content-Type confusion in the Form Trigger/Respond-to-Webhook nodes to read arbitrary files (e.g. /proc/self/environ, the SQLite database, and the config file), from which the attacker derives the JWT secret from n8n's encryptionKey and forges an admin session cookie. That admin access is then used to create a workflow exploiting CVE-2025-68613, an expression-injection sandbox bypass (`this.process.mainModule.require`) that yields command execution, all demonstrated with a working Python exploit script and Docker lab against n8n 1.65.0. It notes the exploit was developed independently of a prior Cyera/Dor Attias write-up on a related n8n chain and details the specific vulnerable workflow pattern (file-upload form + binary Respond node) required for exploitation.

n8nDockerSQLite+1
CVE-2026-21858CVE-2025-68613CVE-2025-68668+2

Offensive Security, AppSecΒ· Added 26 Sep 2026

ccb.belgium.beadvisoryπŸ›‘οΈ Security

Warning: Vulnerability in Starlette framework and related frameworks like FastAPI exposes millions of servers to authentication bypass, Patch Immediately! | CCB Belgium

Belgian CCB advisory on CVE-2026-48710 ("BadHost", CVSS 6.5), an authentication bypass in Starlette versions before 1.0.1. The Host header was not validated when request.url was rebuilt, so request.url.path could differ from the routed path. Middleware and endpoints that enforce access control on request.url could therefore be bypassed. The flaw affects FastAPI, LiteLLM, vLLM, MCP servers and other Python LLM infrastructure, and may expose stored third-party credentials. The advisory recommends upgrading to 1.0.1 or later and increasing monitoring, and links to the badhost.org scanner and to the GitHub, OSTIF, X41 D-Sec and Ars Technica write-ups.

StarletteFastAPILiteLLM+3
CVE-2026-48710BadHostCCB+3

AppSec, AI SecurityΒ· Added 26 Sep 2026

Showing 120 of 256

Show more