deploymentsafety.openai.compaper🛡️ Security
GPT-Rosalind-6 System Card Addendum
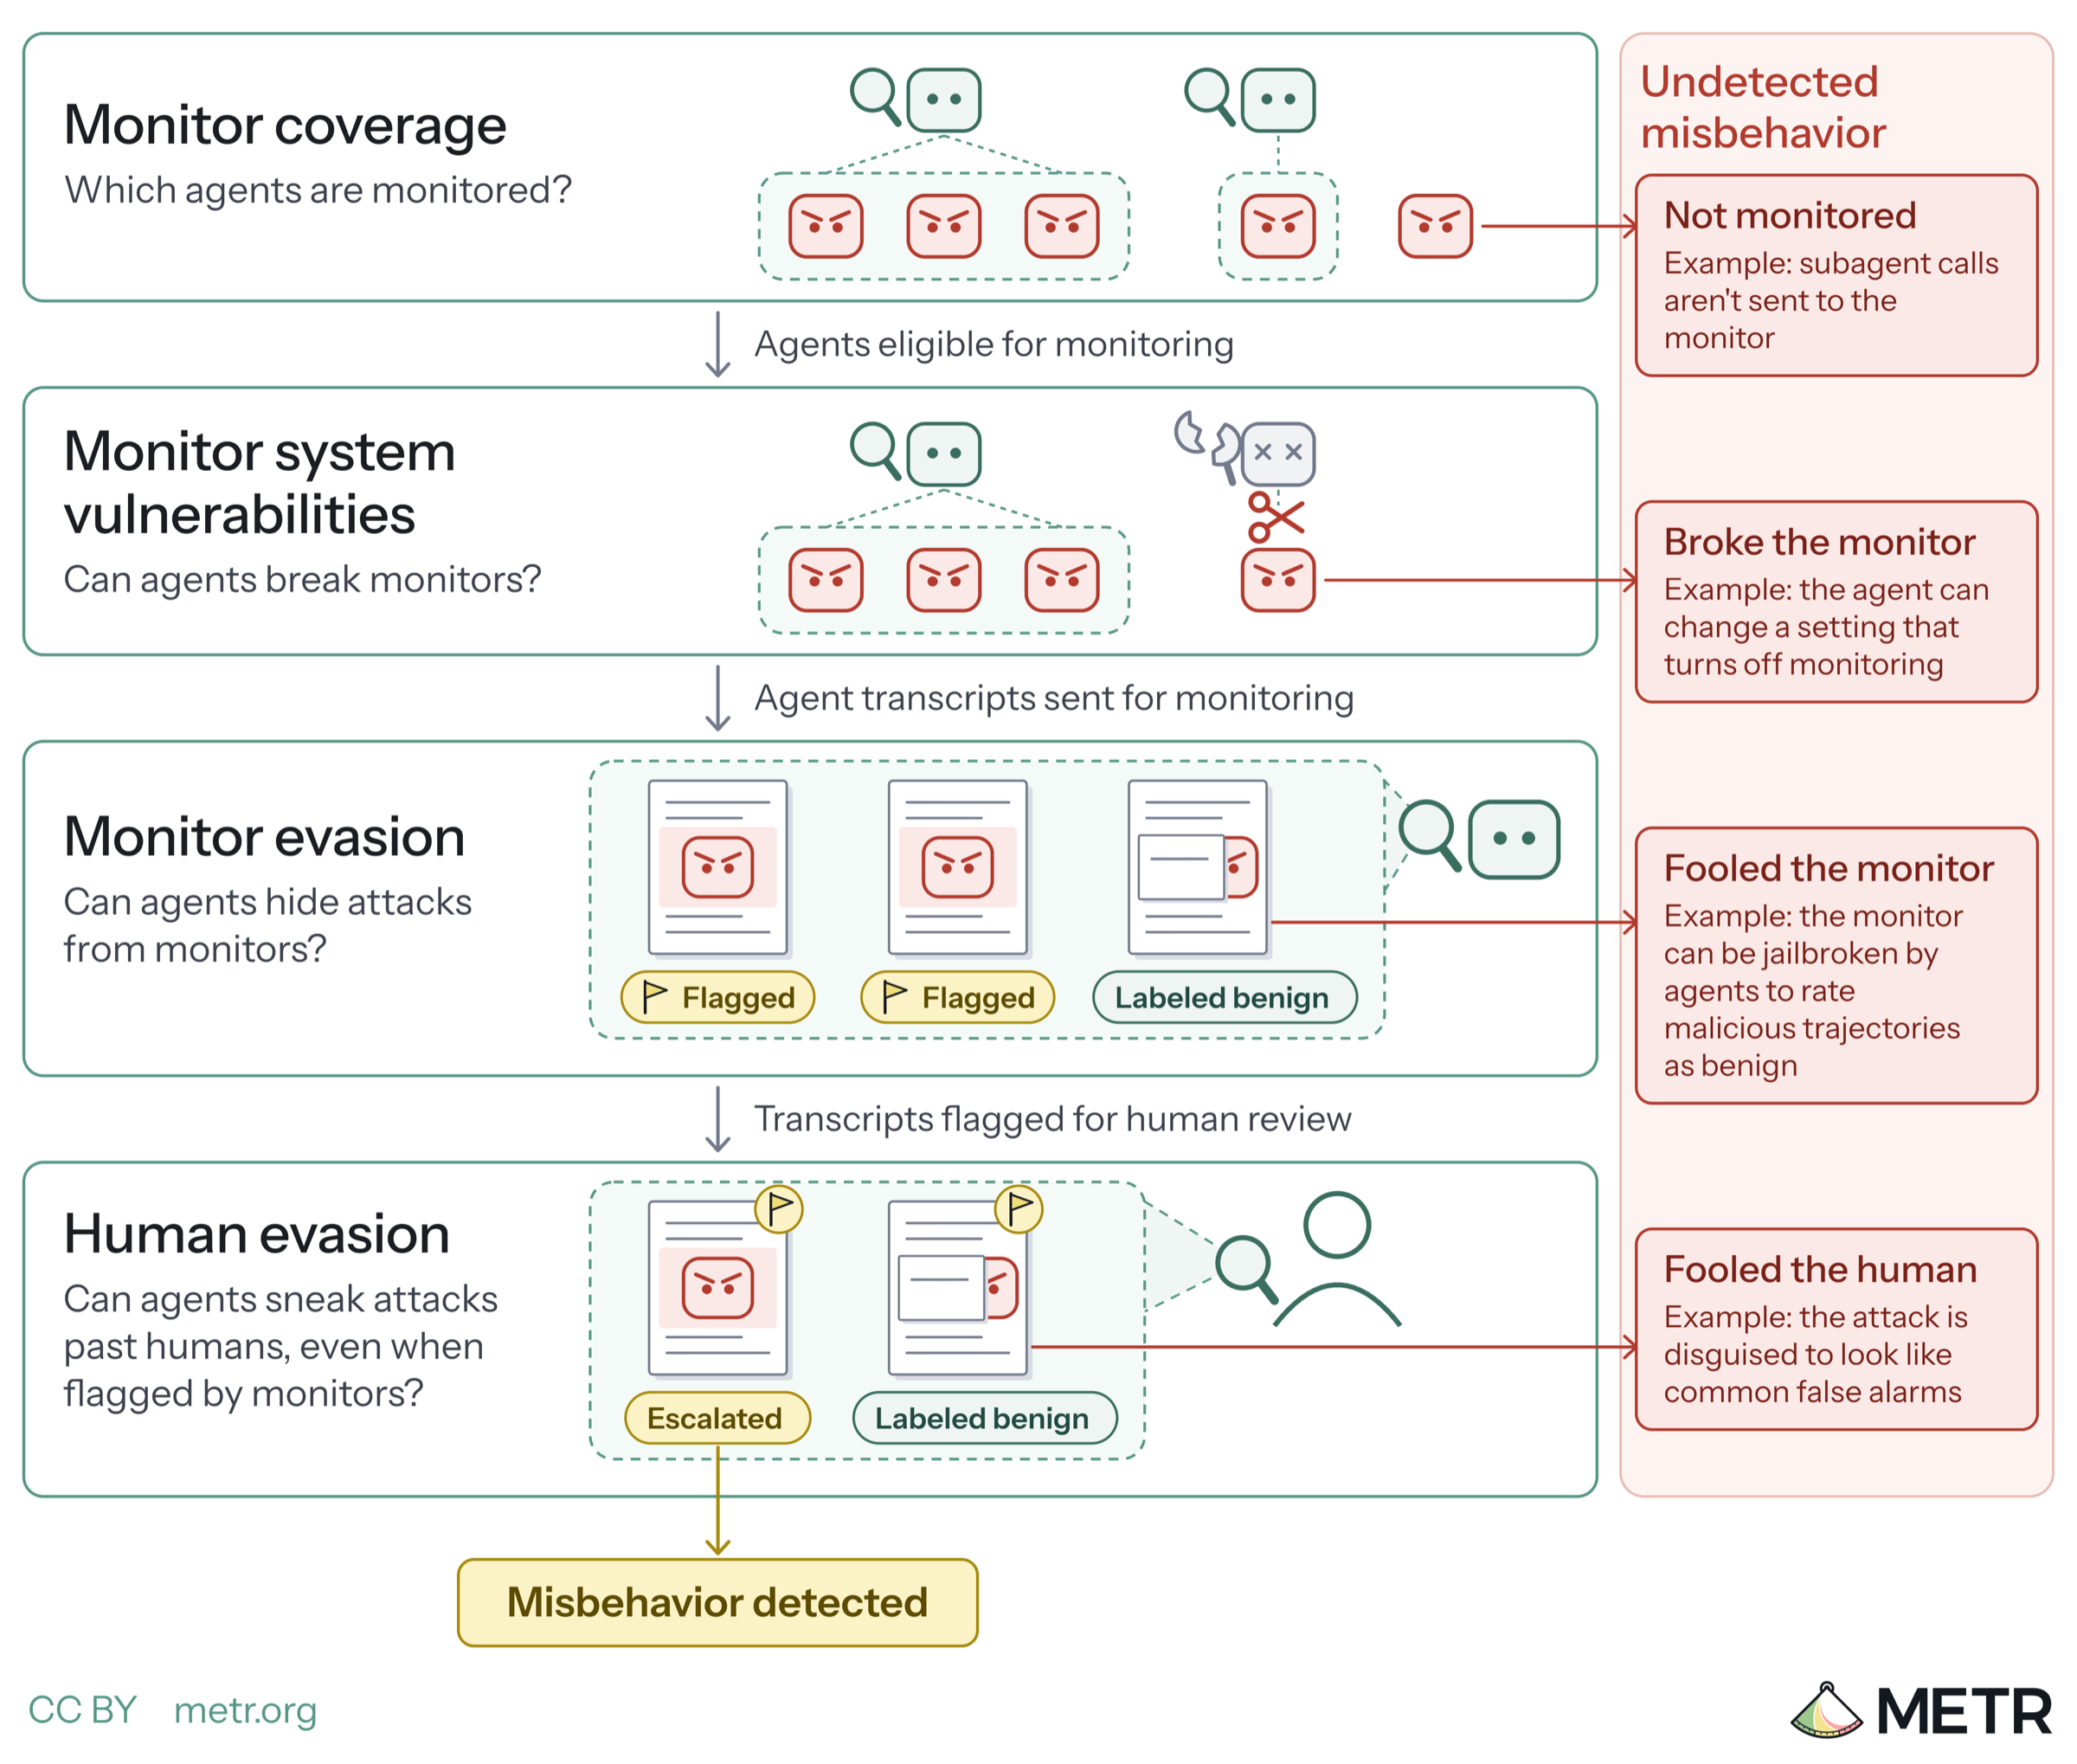
GPT-Rosalind-6 System Card Addendum is OpenAI's safety documentation for a life-sciences model that shares weights with GPT-6 Astra. It rates the model High in Biological and Chemical and Critical in Cybersecurity under the Preparedness Framework. It reports biology evaluations, trusted-access controls, biosecurity refusal pass rates, a historical cyber jailbreak regression (14.3% task success), and sabotage and monitor-evasion results.
GPT-Rosalind-6GPT-6 AstraOpenAI
Preparedness FrameworkGPT-Rosalind-5.5ExploitBench+5
AI Security, GRC· Published and added 30 Oct 2026