Skip to content

90 results for β€œdrop”

What you seeeverything
huntress.comwriteupπŸ›‘οΈ Security

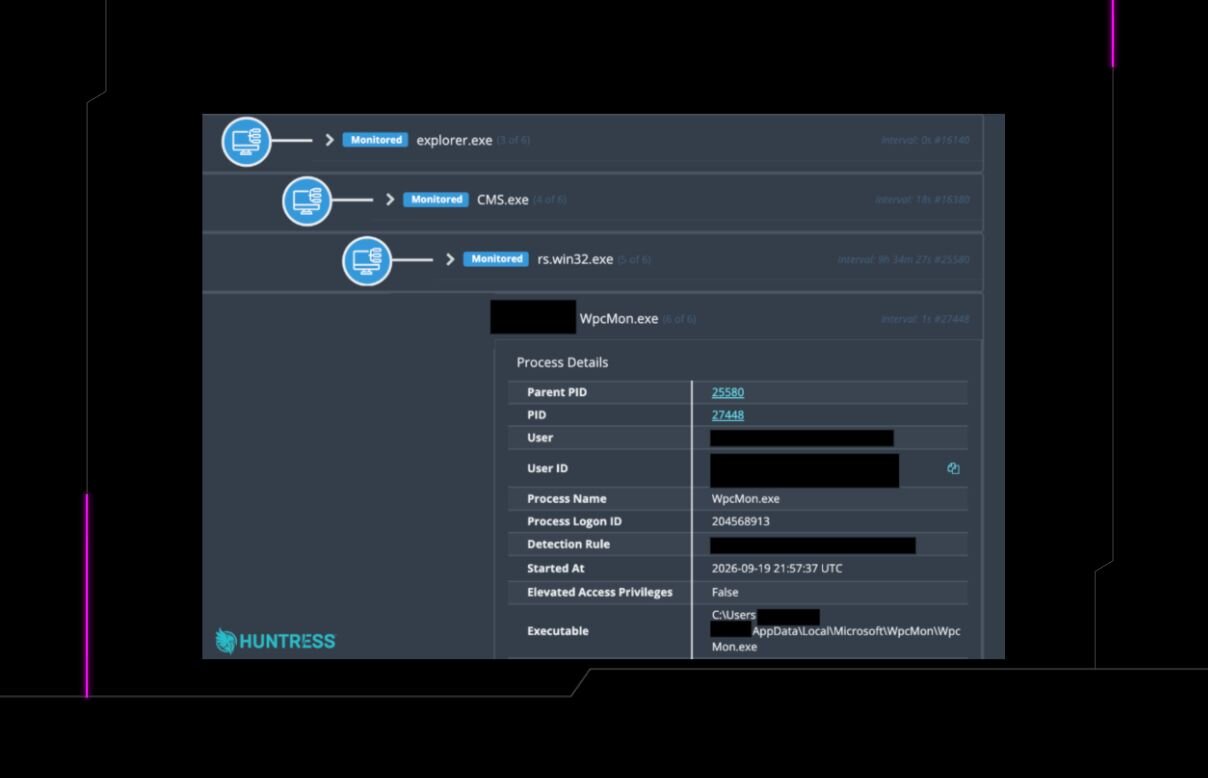
Camera Management Software Compromise Leads to Malware Deployment

Huntress investigation of incidents in September and October 2025 where a compromised camera management application (CMS.exe) was the initial access vector. Attackers dropped rs.win32.exe, a reverse shell, and sideloaded modified zlib DLLs (IPHLPAPI.DLL, samcli.dll) via the legitimate Microsoft WpcMon.exe in AppData, with Run key persistence and beaconing to 144.172.116[.]37. Includes detection pivots and hardening advice.

WindowsHuntress
DLL sideloadingCMS.exers.win32.exe+6

Threat Intel, Blue Team & DetectionΒ· Added 28 Oct 2026, published 27 Oct 2026

stepsecurity.iowriteupπŸ›‘οΈ Security

OVHcloud CLI Compromised via GitHub Release Swap: Detonating the Real GlassWorm Loader and What We Found

Analysis of the 19 October 2026 swap of binaries on five ovh/ovhcloud-cli GitHub releases (v0.11.0 to v0.15.0), live 94 minutes. StepSecurity rebuilt the attacker's binary, detonated the recovered GlassWorm preinstall.js loader against a controlled Solana dead drop, and found install.sh never exposed arm64 Linux, Homebrew was safe, and `ovhcloud version` showing "undefined" identifies the swapped build. Includes IOCs and recovery steps.

OVHcloud CLIGitHubSolana+3
GlassWormForceMemoGHSA-862f-55f5-vmvw+8

Supply Chain, Malware & RE, Threat IntelΒ· Published and added 24 Oct 2026

stepsecurity.iowriteupπŸ›‘οΈ Security

litellm 1.107.0 Compromised on PyPI: Backdoored Wheels Drop a Credential Stealer and an Hourly Remote Code Loader

litellm 1.107.0 was published to PyPI on 21 October 2026 with all seven wheels backdoored through an injected `data = "cook"` maturin build line. The wheels drop cook.pth, cook.py and sitecustomize.py, which run on every Python start. They install a "privcollect" credential stealer (browser, SSH, cloud, AI coding tool and LiteLLM proxy database secrets, sent to litellm.dev) and an hourly GitHub dead-drop remote code loader. The post gives IOCs, detection commands and recovery steps.

LiteLLMPyPIPython+3
privcollectcook.pthsitecustomize.py+6

Supply Chain, Malware & RE, Blue Team & DetectionΒ· Published and added 21 Oct 2026

wiz.iowriteupπŸ›‘οΈ Security

LiteLLM Compromised, Steals Credentials

LiteLLM version 1.107.0 was uploaded to PyPI on 21 October 2026 with a credential stealer, and the same build reached GHCR and Docker Hub images. Wiz describes the three dropped files (cook.pth, cook.py, sitecustomize.py), exfiltration to a fake litellm.dev domain, a GitHub dead drop for a second stage, and the malicious commits pushed through the lookalike Berri-AI repository. The last safe version is 1.106.2.

LiteLLMPyPIDocker+3
Berri-AIcook.pthsitecustomize.py+2

Supply Chain, Threat Intel, AI SecurityΒ· Published and added 21 Oct 2026

boredhackerblog.infowriteupπŸ›‘οΈ Security

Plex vulnerabilities being exploited in the wild to drop a cryptominer

Honeypot writeup of in-the-wild exploitation of Plex Media Server through the Plex2Shell chain (CVE-2026-96652, -96654, -96655, -96656) in October 2026. Attackers from 45.194.92.222, 91.92.40.202 and 176.65.139.228 used SSRF-style timeline/subscribe requests and downloaded a Docker-named dropper and an XMRig miner from 217.60.194.116. Includes file hashes, a later-seen proxyware sample (myawesomeproxy), lab pcaps for signatures and links to sandbox reports.

Plex Media ServerXMRigDocker+1
CVE-2026-96652CVE-2026-96654CVE-2026-96655+8

Threat Intel, Blue Team & DetectionΒ· Added 20 Oct 2026, published 19 Oct 2026

dfir.chwriteupπŸ›‘οΈ Security

Field Notes: EtherRAT Distributed Through a Legitimate Intune Workflow

DFIR case where a malicious MSI impersonating Advanced IP Scanner, sourced from a fake GitHub repo found via Bing, was imported by a customer into Microsoft Intune and deployed to four endpoints, running a Node.js-based EtherRAT chain. It traces the infections by correlating the MSI ProductCode, MDMAppInstaller/omadmclient process ancestry and Intune app inventory (Graph PowerShell query). It also covers renamed node.exe hash-hunting pitfalls, Ethereum RPC dead-drop C2 traffic, a screen-capture script and a second impersonating repo.

Microsoft IntuneNode.jsEthereum+3
EtherRATEtherHidingAtos Threat Research Center+4

Blue Team & Detection, Threat Intel, Malware & REΒ· Added 14 Oct 2026, published 13 Oct 2026

x.comwriteup🧠 AI

Aditya (@adityawaslost) on X

Describes Resolve, a Kaggle benchmark of 16 single-function Python edits. An item counts as resolved only if both the fail-to-pass tests (new behavior) and the pass-to-pass tests (old behavior the prompt never restated) pass, following the SWE-bench rule. A second task, resolve-plus, adds a hidden edge suite. Results for 23 frontier and open models: GPT-6.1 Sol and GPT-5.6 Luna lead at 0.9375 on both tasks, while DeepSeek-R1, Sonnet 5.5 and Opus 5.5 drop from 0.9375 to 0.875. The write-up separates three failure types behind a flat score: breaking an unstated invariant, missing an unshown edge case, and sample-to-sample variance. It also compares score against output price per million tokens.

PythonClaudeGemini+3
Resolveresolve-plusKaggle+23

evals, coding-agentsΒ· Published and added 11 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

Threat Actors Exploit Critical AhsayCBS Flaws to Drop Webshells and XMRig Cryptominer

Huntress documents active exploitation of two AhsayCBS (Ahsay Cloud Backup Server) vulnerabilities being chained together: CVE-2026-105133, an authentication bypass in checkSysPwd, and CVE-2026-105134, an unauthenticated RCE in the Replication Receiver's UpdateReceivers.do endpoint that grants SYSTEM. Attackers use the chain to drop JSP webshells, then deploy a renamed XMRig cryptominer (masquerading as msedge.exe via a modified NSSM binary), a Task-Manager-aware anti-detection PowerShell script, and the vulnerable WinRing0x64.sys kernel driver for hardware-level miner access. Huntress provides IOCs, mitigation guidance (restrict management interface, re-image if compromised) and four Sigma rules targeting each stage of the intrusion chain.

AhsayCBSXMRigSigma+3
CVE-2026-105133CVE-2026-105134WinRing0x64.sys+2

Threat Intel, Blue Team & Detection, AppSecΒ· Added 9 Oct 2026, published 8 Oct 2026

aikido.devwriteupπŸ›‘οΈ Security

tensorlake NPM package compromised with Shai Hulud worm

Aikido details a new Shai-Hulud worm wave that compromised the tensorlake npm package (v0.5.144, 100k+ lifetime installs) via a hijacked GitHub maintainer identity. The malware's preinstall script drops the Bun runtime to run an obfuscated payload that exfiltrates CI/cloud secrets, browser crypto-wallet extension data (via a bundled HackBrowserData binary), uses a blockchain dead-drop (an Ethereum contract queried via public RPC nodes) to resolve a fallback C2, and includes a GitHub-token-triggered dead-man's switch that wipes infected machines. The post includes full IOCs: file hashes, the C2 domain iseekaigogo[.]com, and the threat actor's wallet/contract addresses.

npmBunEthereum+3
Shai-Huludtensorlakeiseekaigogo[.]com+4

Supply Chain, Malware & REΒ· Published and added 8 Oct 2026

socket.devwriteupπŸ›‘οΈ Security

TensorLake npm SDK Compromised in ChainDrop Shai-Hulud Credential-Stealing Attack

Socket.dev reports that TensorLake's npm SDK was compromised as part of the ChainDrop campaign, a variant/wave of the Shai-Hulud credential-stealing npm worm. The compromised package reportedly harvests developer credentials from infected systems, continuing the pattern of self-propagating npm supply-chain attacks seen across the Shai-Hulud family. Full technical detail could not be verified in this pass due to a content-processing failure.

npmSocket
TensorLakeChainDropShai-Hulud

Supply ChainΒ· Published and added 8 Oct 2026

watchtowr.comwriteupπŸ›‘οΈ Security

Post-Exploitation Analysis & Artifacts – Citrix NetScaler CVE-2026-88771

watchTowr post-exploitation analysis of CVE-2026-88771, an unauthenticated log-poisoning command injection in Citrix NetScaler (advisory CTX697096). Sensors logged thousands of attempts: about 85% were OOB callbacks, the rest Sliver implants, a trojanized Dropbear SSH backdoor, a Perl stager with a PHP webshell, and SSH-key and secret-harvesting sprays. Includes artifacts to hunt (/var/tmp files, ns_helper, ns.conf edits) and IOC repo pointers.

Citrix NetScalerSliverSSH+2
CVE-2026-88771CVE-2026-88772CVE-2026-88779+8

Threat Intel, Blue Team & Detection, Malware & REΒ· Added 30 Oct 2026, published 7 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue RMMs

Huntress details a phishing campaign that abuses legitimate Microsoft Power BI dashboards (app.powerbi.com) to host a fake "Download Reference" lure that bypasses mail filters trusting the Microsoft domain. Clicking the lure triggers browser/environment fingerprinting and Telegram-bot-based victim telemetry exfiltration via attacker domains (dailylifeproject.site, burnsworth.site, etc.), then silently downloads rogue ScreenConnect installers; a chained CMD/PowerShell script (SCAutoFix.ps1) deploys a second ScreenConnect instance, uninstalls the first for evasion, drops the defense-evasion tool HideUL_x64.exe, and sets a recurring scheduled task before Huntress's SOC intervened.

Power BIScreenConnectTelegram+3
HideUL_x64.exeSCAutoFix.ps1SCAutoRepairEvery2Min

Threat Intel, Blue Team & DetectionΒ· Published and added 7 Oct 2026
fiveminutesforward.comwriteup🧠 AI

Write Like It's 1866: LLMs Relearn Telegraphese

The author revives "cablese," the terse telegraph-era writing style, as an LLM prompting technique: instructing a model to write dense, article-dropping summaries cuts output tokens 25–49% depending on model family, while downstream models (including ones never shown the instruction) answer comprehension questions from the compressed text at parity or better than from plaintext. The piece introduces the "Telegraph Test," an open benchmark (github.com/Travis42/telegraph-test) with ~1,300 questions over 50 passages and a fixed deterministic grader, used to measure compression ratio, cross-model legibility, and read-back/decode costs for GLM-5.3-Flash, Gemma, Qwen and gpt-5-mini; it also contrasts this human-readable, auditable register against emergent machine-only compression protocols described in other papers (BabelTele, GLOSSOGEN) and existing tools (Terse, Caveman).

GLMGemmaQwen+1
GLM-5.3-Flashgpt-5-miniZ.ai+4

prompting, evals, ai-infraΒ· Published and added 7 Oct 2026

theravenfile.comwriteupπŸ›‘οΈ Security

CITRIX 0-DAY EXPLOITS: CVE-2026–88771 & CVE-2026–88772 IN THEΒ WILD

An incident-response style deep dive into active in-the-wild exploitation of Citrix NetScaler ADC/Gateway via CVE-2026-88771 (unauthenticated RCE through log-poisoning of ns_monuploadd_err.pl) and CVE-2026-88772 (DTLS memory overflow), part of 8 CVEs disclosed by Citrix on September 27, 2026. The author reverse-engineers the full post-exploitation toolkit dropped after root is obtained: SLAPSHOT (a Perl/Python loopback TCP tunneler/pivot), WHIPSHOT (a disguised PHP web shell served via fake CSS paths), the Platypus C2 agent, and a Perl "Pitboss" dropper script (with full decoded source and an embedded SHA-256-protected PHP web shell) that creates a rogue superuser, SUIDs /bin/sh, exfiltrates NetScaler config, and patches httpd.conf for persistence. It closes with extensive IOCs (C2 IPs, file hashes, paths, credentials) and patch guidance for affected NetScaler builds.

Citrix NetScalerPHPPython+2
CVE-2026-88771CVE-2026-88772CVE-2026-88773+10

Threat Intel, Malware & REΒ· Published and added 6 Oct 2026

rapid7.comwriteupπŸ›‘οΈ Security

SMTP is the key: BPFDoor and AVERAT hitting the network edge

Rapid7 details a new BPFDoor campaign targeting telecom and network-edge appliances (ShareTech, SpamSniper mail gateways) and a six-sample Linux RAT family dubbed AVERAT found on compromised Taiwanese CPE (Synology NAS, a NetKlass device, a Dahua DVR). The writeup reconstructs the Rapid7 BPFDoor controller's HTTP-tunneled trigger mechanism, a fileless ShareTech dropper that stages binaries as ntpdate/udevds and deletes them while processes keep running, a BPF Rekoobe variant that hides inside SMTP port-25 traffic, and AVERAT's RC4-derived config/C2 scheme β€” tying the infrastructure to the broader China-nexus ORB (Operational Relay Box) device pattern described in CISA/NCSC-UK advisory AA26-113A. It closes with detection guidance for unlinked/deleted process execution, dropper staging artifacts, and port-25 C2 callbacks, plus full IOC and ATT&CK tables.

LinuxeBPFYARA+2
BPFDoorAVERATRekoobe+11

Malware & RE, Threat Intel, Blue Team & DetectionΒ· Added 7 Oct 2026, published 2 Oct 2026
socket.devwriteupπŸ›‘οΈ Security

Pretty Themes, Hidden Loaders: GlassWorm-Linked Extensions Span VS Code Marketplace and Open VSX

Socket's Threat Research team uncovered a theme-extension cluster spanning four VS Code Marketplace and six Open VSX listings, including two confirmed malicious extensions: Aurora Nocturne Night Theme (a Windows downloader that fetches and silently executes temp_batch.cmd via cmd.exe from fingercakes4sale[.]store, tied to XWorm C2 infrastructure) and Cosmic Nebula Themes, whose app.js decrypts an AES-256-CBC embedded stage and uses a Solana transaction memo as a dead-drop to resolve follow-on payload infrastructure β€” the same AES key, Solana address, and execution model previously documented in GlassWorm activity. Git commit identities, near-identical theme source, shared Russian-language developer comments, and brandjacking (Coca-Cola, Aurora Borealis name-squatting) link the cluster together; a Dec 14, 2025 DEV Community article is assessed as promotional infrastructure driving Open VSX installs. The post provides full IOCs (hashes, domains, Solana address, AES key/IV, GitHub accounts) and MITRE ATT&CK mappings for defenders to hunt and inventory extensions across both registries.

VS CodeOpen VSXSolana+3
GlassWormXWormAurora Nocturne Night Theme+13

Supply Chain, Malware & RE, Threat IntelΒ· Published and added 2 Oct 2026
blog.talosintelligence.comwriteupπŸ›‘οΈ Security

China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor

Cisco Talos details UAT-11587, a China-nexus threat cluster targeting government, defense, and policy organizations across Taiwan, India, the Philippines, Cambodia, and other Asian countries with spear-phishing and a five-stage infection chain (HTA/WSF stagers, JScript decryptors, .NET BinaryFormatter/ActivitySurrogateSelector deserialization gadgets, and DLL sideloading via the signed GatherOsState.exe) to deploy a new Rust-compiled backdoor called Antino. Antino uses Microsoft Graph/Outlook/OneDrive as a dead-drop C2 channel instead of a traditional C2 server, supports shell/PowerShell execution, file transfer, shellcode loading with a sleep-mask evasion technique, and abuses the Windows Scripted Diagnostics framework for persistence; Talos also notes possible infrastructure overlap with Symantec's "Jewelbug" cluster and Arctic Wolf's UNC6384 reporting. Includes ClamAV/Snort coverage and IOCs.

RustMicrosoft 365PowerShell+4
UAT-11587AntinoJewelbug+5

Threat Intel, Malware & REΒ· Added 7 Oct 2026, published 30 Sep 2026
huntress.comwriteupπŸ›‘οΈ Security

Determined Attacker Uploads Malicious Webshells to Parks and Rec Management Platform Servers

Huntress details a four-act intrusion against a shared parks-and-recreation management platform running on IIS, where an attacker first tried noisy unauthenticated exploits (IIS 8.3 tilde enumeration, WebDAV verb abuse, upload-handler bypasses) before simply registering a member account and uploading .aspx webshells via a member-file upload feature across three servers. The attacker enumerated hosts, extracted web.config/connection strings, hunted for cardholder data (Fortis/MXMerchant webhook logs, CVV/card-number strings), then escalated to timestomping, re-deploying known-filename webshells, and finally injecting an AI-generated PowerShell/JS dropper into a trojanized jQuery file to turn site visitors' browsers into WebRTC/WebSocket C2 clients (ririmochii/bubuneeko Cloudflare Workers infrastructure). Includes a zh-CN PowerShell user-agent string used for attribution and full command/IOC listings useful for detection engineering.

IISPowerShellWindows+3
ririmochii[.]workers[.]devbubuneeko[.]workers[.]devIIS 8.3 tilde enumeration+2

Threat Intel, Blue Team & Detection, Offensive SecurityΒ· Added 1 Oct 2026, published 30 Sep 2026
microsoft.comwriteupπŸ›‘οΈ Security

Phishing Abuses RMM Tools for Persistent Access

Microsoft Defender Experts document a July 2026 phishing campaign that delivers a masqueraded but legitimately signed MSP360 RMM installer (v2.5.0.67) via meeting-invite, Zoom, Adobe, and DHL-themed lures hosted on both attacker infrastructure and legitimate cloud services (S3, Cloudflare R2, Dropbox, GitLab, Supabase). After UAC-elevated installation and service persistence, the RMM.Agent.exe service launches PowerShell to silently install a ConnectWise ScreenConnect client via msiexec, which the actor then uses via RunFile to drop credential-theft and reconnaissance tools disguised as Windows/Defender/Phone Link components. A separate July intrusion used FaronicsDeployAgent.exe the same way to deploy ScreenConnect, showing the technique is not MSP360-specific; Microsoft provides IOCs, hunting queries, and mitigation guidance (Application Control, AppLocker publisher rules, ASR rules) but does not attribute the activity.

MSP360ScreenConnectPowerShell+3
T1583.001T1583.006T1566.002+16
Threat Intel, Blue Team & DetectionΒ· Added 7 Oct 2026, published 29 Sep 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

PolinRider is A/B Testing its Way Past Your Detections

Opensourcemalware.com traces PolinRider, a DPRK-linked supply-chain malware delivered via a poisoned .vscode/tasks.json that autoruns an obfuscated payload disguised as a Font Awesome .woff2 file, through an 8-month infection of three real GitHub repos (Binary-Mindz org). Using GitHub's server-side activity log they reconstruct 853 force-pushes showing the operators A/B-testing multiple concurrent payload variants (400/500/900), rewriting commits to impersonate legitimate cleanup commits, hiding payloads inside eslint.config.mjs and prisma.config.ts, and using an Ethereum-wallet-based C2 dead-drop (NullReceiver). The post lists why common detection heuristics (filename search, whitespace padding, marker strings) fail against the new variants and gives working detections (file-type checks, folderOpen task grepping, activity-log force-push monitoring) plus full IOCs.

VS CodeGitHubNode.js+2
PolinRiderDPRKContagious Interview+2

Threat Intel, Supply Chain, Blue Team & Detection, Malware & REΒ· Published and added 26 Sep 2026

gambit.securitywriteupπŸ›‘οΈ Security

Autonomous AI Agents Hack Online Retailers for $25 a Company

Gambit Security recovered the staging server of a financially motivated actor running three open-source AI agent harnesses β€” Strix (vuln scanning), Cairn (autonomous exploitation), and Hermes (orchestration) β€” against hundreds of online retailers at a marginal cost of tens of dollars per target. The campaign exfiltrated 600,000+ credit card records via Magento database compromises, deployed checkout-page card skimmers on at least 19 confirmed and 100+ further sites, and in one case an agent's own cleanup routine dropped 180 database tables including victim backups. The report details full attack chains (SQLi to RCE to AWS Secrets Manager dump to card decryption), the AI harnesses' operating costs (~$25 mean per target on OpenRouter/opus-4.6/GLM/DeepSeek), and multiple real-world skimmer injection techniques.

StrixCairnHermes+3
Overwatch DataShadowserver FoundationDaniel Gordon+3

Threat Intel, AI Security, Offensive SecurityΒ· Added 26 Sep 2026, published 22 Sep 2026

aikido.devwriteupπŸ›‘οΈ Security

Graphalgo campaign spreads to Terraform providers and Go Modules

Aikido documents the Graphalgo malware campaign's expansion beyond NPM into two malicious Terraform providers (gocommunity-io/dockerd and the kreuzwerker/docker typosquat kreuzwenker/docker) and two Go modules (gocommunity.io/orderedbtree, gogets.dev/btreex), marking the first observed systematic Terraform provider malware distribution. The payload is a Go port of Graphalgo sharing blockchain infrastructure, Slack C2, and a public key with prior JS/NPM samples; it activates only under specific hash-gated runtime conditions (targeted attack indicator), then deploys a Go RAT with dual C2 channels β€” an Ethereum (Arbitrum Sepolia) smart-contract dead drop and Slack bot messaging β€” plus self-delete and remote code execution capabilities. The threat actor also stood up two fake Go package ecosystem websites (gocommunity.io, gogets.dev) to socially engineer developers and backdated Git commits to obscure module publication timing.

TerraformGoSlack+3
GraphalgoReversingLabsSafedep+6

Supply Chain, Threat Intel, BlockchainΒ· Published and added 22 Sep 2026

huntress.comwriteupπŸ›‘οΈ Security

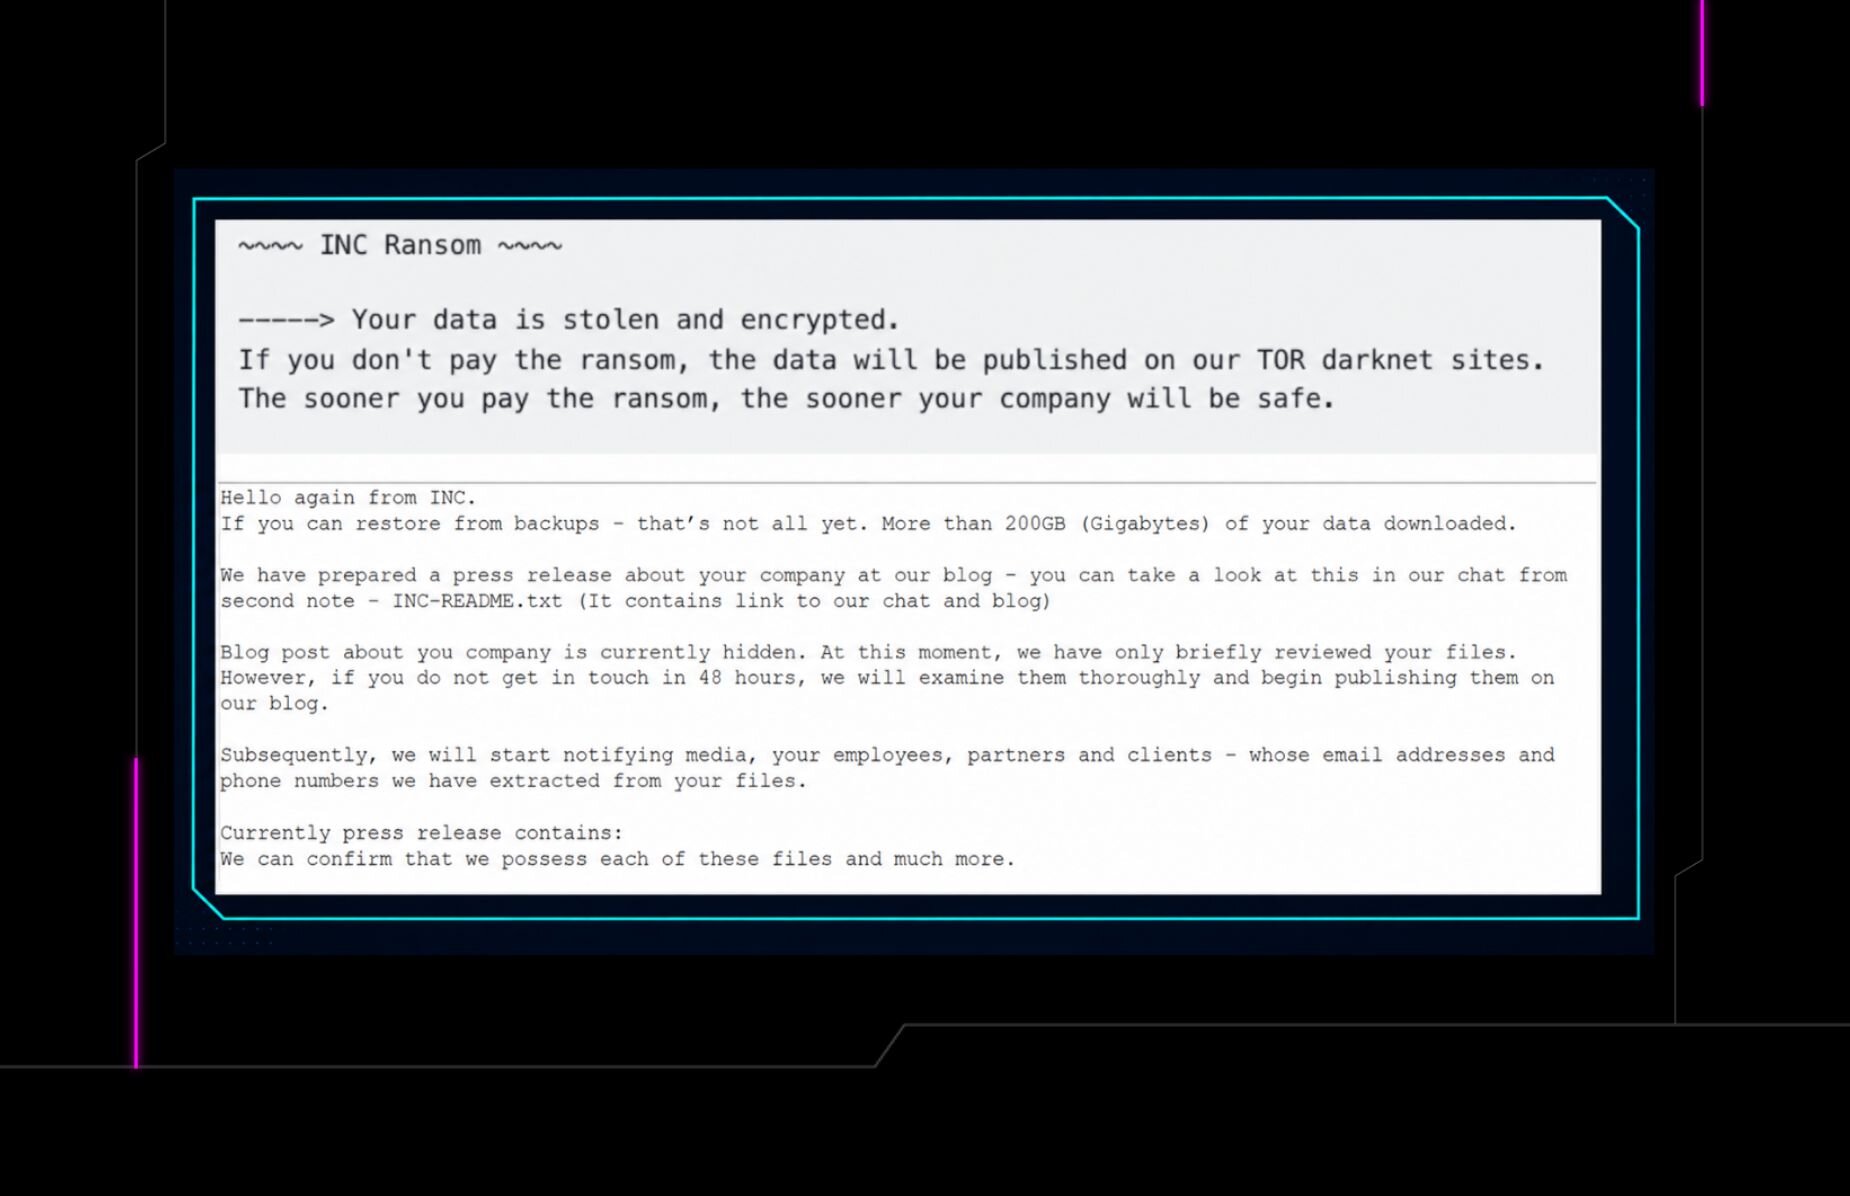
The Tale of Two INC Ransom Notes: A Ransomware Timeline | Huntress

Huntress details a post-incident investigation into an INC ransomware attack that hit 175+ endpoints, reconstructed from surviving EDR telemetry and Windows event logs rather than live detection. The intrusion shows a 17-day gap between initial scheduled-task persistence and RDP lateral movement (possibly an initial access broker), and a second wave using AnyDesk, a BYOVD tool (hwau.exe loading the HwAudio kernel driver) to disable security controls, and Impacket's atexec.py to deploy INC ransomware. Attackers dropped two distinct ransom notes 53 minutes apart: a standard INC-README.txt and a detailed DATALEAK_PRESS_RELEASE.txt threatening to notify media, employees and partners with a full inventory of stolen files.

AnyDeskImpacketPowerShell+3
INC ransomwareBYOVDnetscan.exe

Threat Intel, Blue Team & DetectionΒ· Added 22 Sep 2026, published 21 Sep 2026

socket.devwriteupπŸ›‘οΈ Security

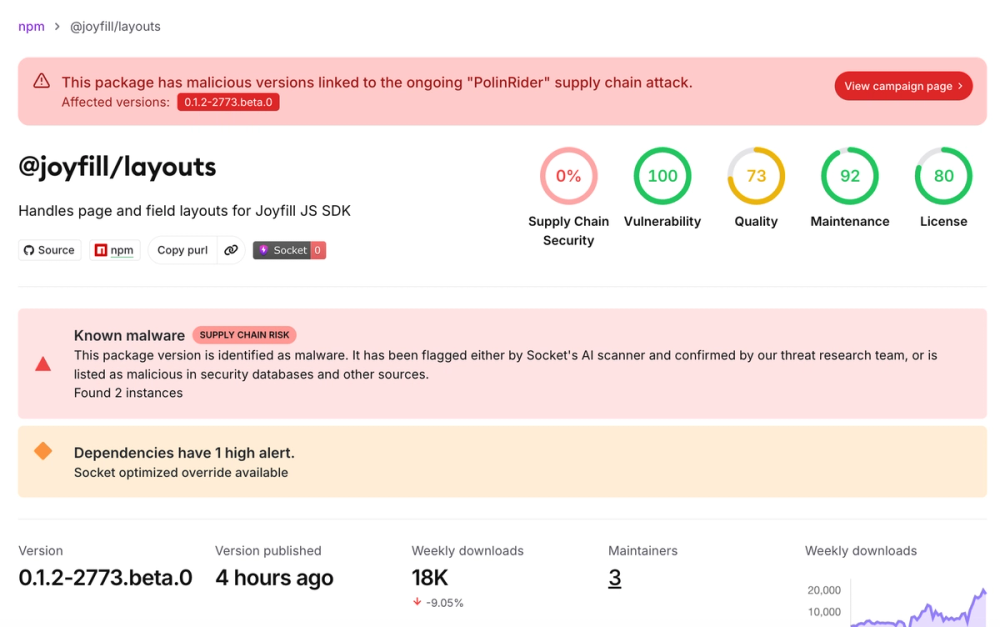
Socket: Two Joyfill npm Beta Releases Compromised to Deliver DEV#POPPER Remote Access Trojan

Socket's research team found two beta releases of the @joyfill npm packages (@joyfill/layouts and @joyfill/components) contained an import-time JavaScript implant that resolves encrypted payloads through Tron, Aptos, and BNB Smart Chain transactions, ultimately dropping a 77KB Node.js remote-access trojan matching the DEV#POPPER family and sharing loader fingerprints with the PolinRider blockchain-loader campaign. The RAT establishes a Socket.IO C2 channel, executes arbitrary JS/shell commands, exfiltrates files and clipboard data, and persists by patching files inside VS Code, Cursor, Antigravity, Discord Desktop, GitHub Desktop, and the global npm CLI; a parallel detached-process branch fetches an additional bootstrap that can deploy a Python credential/browser-data stealer assessed as an OmniStealer variant. Because the implant fires on module load (not via npm lifecycle scripts), `--ignore-scripts` provides no protection, and the writeup includes full IOCs, blockchain addresses, C2 infrastructure, and MITRE ATT&CK mappings.

npmNode.jsPython+3
DEV#POPPERPolinRiderOmniStealer+12

Supply Chain, Malware & RE, Threat IntelΒ· Added 22 Sep 2026, published 20 Sep 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

WeaselBiscuit Strips BeaverTail and OtterCookie Down to Essentials

OpenSourceMalware researchers detail WeaselBiscuit, a newly discovered lightweight JavaScript infostealer found hidden in 11+ npm packages (e.g. process-tailwind, engin1, the @biz44 scope), which shares tradecraft with DPRK-linked BeaverTail/OtterCookie but strips out wallet-draining, password decryption, and remote-shell features. The writeup walks through the full infection chain - a package auto-running a detached Node loader, fetching a Base64-encoded second stage from Npoint dead-drop URLs, and beaconing to a hardcoded HTTP C2 (103.170.217.184:8787) - plus its capabilities (Chrome extension-storage theft, clipboard capture, Windows keylogging) and a campaign-cluster graph tying packages together via shared hashes and resolver URLs. Attribution to DPRK is explicitly labeled a tentative hypothesis rather than confirmed.

npmNode.jsChrome
WeaselBiscuitBeaverTailOtterCookie+3

Supply Chain, Threat Intel, Malware & REΒ· Published and added 17 Sep 2026

group-ib.comwriteupπŸ›‘οΈ Security

HEAVYGRAM: A Telegram-based Surveillance Backdoor Linked to Handala Hack

Group-IB documents previously undocumented samples of HEAVYGRAM, a Python/PyInstaller-based Windows backdoor that uses the Telegram bot API for command-and-control, screen/audio capture, data exfiltration, and DLL side-loading, alongside the related CRUDEEXCLUDE loader that adds Windows Defender exclusions. The research corroborates and extends a March 2026 US DOJ affidavit and FBI FLASH report, attributing the malware with moderate confidence to the Handala Hack persona β€” assessed as a false-flag "hacktivist" front for Void Manticore (aka Storm-0842/Banished Kitten), operating on behalf of Iran's MOIS β€” used since Fall 2023 against Iranian dissidents, journalists, and critics of the Iranian government via Telegram-delivered, Delphi-packaged lures (fake KeePass, Telegram, Pictory apps). It details four infection-chain variants (WSF/VBS downloaders, HTA Telegram-polling scripts, Delphi droppers with embedded archives), the implant's command prefixes (@@/**/##) and attachment handlers, dual-bot C2 configurations, and provides IOCs and detection/hardening recommendations.

TelegramPowerShellPython+3
Handala HackVoid ManticoreStorm-0842+12

Threat Intel, Malware & REΒ· Added 1 Oct 2026, published 17 Sep 2026

endorlabs.comwriteupπŸ›‘οΈ Security

Shai-Hulud 2 Malware Campaign Targets GitHub and Cloud Credentials Using Bun Runtime | Blog | Endor Labs

Endor Labs' live incident tracker for the Shai-Hulud 2.0 npm supply-chain worm that began around Nov 24, 2025, compromising packages from Zapier, ENS Domains, Postman and PostHog. It details the infection chain (malicious preinstall script, setup_bun.js dropper, obfuscated bun_environment.js payload), TruffleHog-style credential theft from AWS, GCP, Azure, GitHub and npm, self-replication via stolen npm and GitHub tokens, a self-hosted GitHub Actions runner backdoor abusing repository Discussions for command injection and C2, and destructive wiper behavior that shreds the user's home directory on Windows and Linux.

npmBunGitHub Actions+3
Shai-Hulud 2.0Shai-HuludZapier+3

Supply Chain, Threat Intel, DevSecOpsΒ· Published and added 11 Sep 2026

blog.talosintelligence.comwriteupπŸ›‘οΈ Security

Active exploitation of Cisco Secure Firewall Management Center vulnerabilities

Cisco Talos details active exploitation of CVE-2026-20079 (CVSS 10.0 unauthenticated auth bypass leading to root) and CVE-2026-20316 (low-privilege login via static credentials) in Cisco Secure Firewall Management Center. Three post-compromise clusters are tracked: UAT-12197 deploying a JSP web shell and JAR command executor to exfiltrate credentials; UAT-11823, overlapping with Sandworm, using a malicious Makeself license.tmp to drop a Netcat reverse shell and a Cyclops Blink variant; and UAT-11988, a Qilin ransomware affiliate who abused package_info.pl for LOTL recon, SOCKS5/reverse-SSH tunneling, and ultimately deployed Qilin ransomware. Talos provides Snort SIDs, hotfix guidance ahead of a comprehensive hardening release, and a GitHub IOC repository.

Cisco Secure Firewall Management CenterImpacketInvoke-TheHash+3
CVE-2026-20079CVE-2026-20316UAT-12197+6

Threat Intel, Offensive SecurityΒ· Added 7 Oct 2026, published 9 Sep 2026

huntress.comwriteupπŸ›‘οΈ Security

Grand Theft Auto VI hype leads to malware

Huntress analyzed a fake GTA6 game ISO (some padded to 100GB+ with junk data) distributed via SEO poisoning, gaming forums, and torrents ahead of the game's real release. The ISO's "installer" drops a Russian-language crack-themed installer that stages multiple NJRAT copies, a DCRAT implant, the Mercurial Grabber infostealer (exfiltrating browser/Discord/Roblox/Minecraft data via Discord webhooks), Chaos ransomware repurposed as a destructive wiper (with a fake "license not found" error to mask the compromise), and an unexplained Yandex Browser install. The writeup includes IOCs (C2 IPs, ngrok tunnel, hosts-file modifications, malicious Discord webhook URL) and notes current Windows Defender detects the components.

WindowsWindows DefenderMicrosoft Edge
NJRATDCRATMercurial Grabber+2

Malware & RE, Threat IntelΒ· Added 11 Sep 2026, published 9 Sep 2026

blog.talosintelligence.comwriteupπŸ›‘οΈ Security

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager

Cisco Talos reconstructs two related WebDAV-based infection chains (tracked actor UAT-10820) that use a ClickFix fake-CAPTCHA lure, EtherHiding on BNB Smart Chain to stage JavaScript via a malicious Cloudflare Worker, and WebDAV-delivered disguised DLLs executed via rundll32 ordinal calls to drop the Amatera stealer. Depending on the C2 configuration, Amatera then deploys either a NativeAOT-loaded ZigCryptoStealer with a BYOVD EDR-killer driver and a Go-based Yamux reverse proxy, or a PowerShell stager that installs a trojanized NetSupport Manager RAT pointed at Russian C2 infrastructure. The post details loader internals, Amatera's dead-drop C2 resolution via Telegraph and Steam, and provides ClamAV signatures plus a full IOC list.

WebDAVPowerShellGo+3
UAT-10820AmateraZigCryptoStealer+8

Threat Intel, Malware & RE, BlockchainΒ· Added 7 Oct 2026, published 8 Sep 2026

Showing 30 of 90

Show more