[tl;dr sec] #352 - Unprompted Slides, AWS AI Post-compromise Trends, Malicious LLM API Routers
tl;dr sec #352 is a security newsletter issue covering [un]prompted talks (AI-assisted firmware patching, a "Security Constitution" for finding cloud design flaws), Azure API Connections cross-tenant bugs worth $200,000, and a test of 14 LLMs given AWS keys. It also covers a paper on malicious LLM API routers (9 of 428 injecting code) and Datadog's "counterfeit policy" bypass of the Jev classifier.
 tldrsec.comarticleAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 GitHub saw 7.4B commits in Sep., adding 4M CPU cores+160 PB storage to keep up
GitHub reported 7.4 billion commits per month in September 2026, up from 2.9 billion in August and 1.4 billion in April, which it attributes mostly to agentic demand. It has added 4 million CPU cores, 160 PB of storage and 50 Tb/s of network capacity this year, mostly on Azure. It is also rearchitecting to separate compute and storage, with internal benchmarks showing up to 35x higher write throughput.
 thenewstack.ioarticleAdded 30 Oct 2026, published 28 Oct 2026🧠 AI
 GitHub Universe 2026: Evolving every layer of the stack
GitHub Universe 2026 recap in which GitHub presents its agentic software delivery vision and new Copilot products: the Copilot app, Copilot Fusion multi-model routing, Copilot projects, session continuity, automations that learn from outcomes, and code review Max. GitHub Enterprise customers can use all Copilot features without a separate subscription. GitHub also reports added capacity, a multi-region Azure migration and a redesigned Git architecture.
 github.blogarticleAdded 29 Oct 2026, published 28 Oct 2026🧠 AI
 The hidden network: Inside the phishing infrastructure ecosystem powering global cybercrime
Microsoft Threat Intelligence maps a Chinese-language cybercrime ecosystem: the YAM Store (Storm-3119), an initial access broker that hijacks Microsoft 365/Azure Education tenants and resells accounts, licenses and SharePoint/OneDrive storage, and the Storm-2990 phishing kits (CoGUI, Haozi, Iron Man System) sold via Telegram. It details the five-stage broker pipeline (app-only client-secret abuse, PnP Management Shell service principal, Graph permissions, Cloudflare DNS management), kit evasion features (geofencing, fake CAPTCHA, WebSocket/Telegram live interaction, 2,335+ templates), downstream device-code phishing and card fraud, and lists mitigations such as passkeys, phishing-resistant MFA and Conditional Access. Microsoft's DCU facilitated a disruption with law enforcement; kits sent over one billion messages since January 2026.
 microsoft.comarticlePublished and added 14 Oct 2026🛡️ Security
 Microsoft Disrupts Chinese-Language Phishing Market Behind 1B+ Messages
Microsoft and Health-ISAC seized domains tied to YAM Store (Storm-3119), an access broker that hijacks Microsoft 365 and Azure for Education tenants, and to the Storm-2990 phishing kits CoGUI, Haozi and Iron Man, under a Southern District of Florida order. The services sent over 1B malicious messages since January 2026 to 75,000+ organizations in 150+ countries; Microsoft disabled 20,000+ accounts and is blocking 100,000+ domains. Iron Man offers 2,335+ templates and real-time OTP capture, and Resecurity found it needs regular contact with a vendor licensing server, a dependency defenders can exploit.
 securityweek.comarticlePublished and added 14 Oct 2026🛡️ Security
 CISO perspectives on managing vulnerability risks in the age of AI
A Microsoft Security Blog post arguing that frontier AI models are flooding security teams with far more vulnerability findings than human triage was built for, citing a record near-1,000 vulnerabilities disclosed on the September 2026 Patch Tuesday. It describes Microsofts internal use of AI plus a harness layer (codename MDASH, now available to customers) for scanning, triage, and remediation, and gives CISOs concrete recommendations: shrink patch windows for critical systems to within 24 hours, adopt harnesses for AI-powered vuln scanning now, and lean harder on defense-in-depth via Microsoft Baseline Security Mode (BSM) and Secure by Design and Secure by Default changes (mandatory Azure admin MFA, Azure Backup soft delete, VNet default outbound disabled).
microsoft.comarticleAdded 7 Oct 2026, published 6 Oct 2026🛡️ Security GPT-6 Sol on Codex: average scores, quarter the cost | Blog | Endor Labs
Endor Labs ran Codex CLI with OpenAI's GPT-6 Sol on its Agent Security League tasks (200 real-world coding tasks drawn from historical security fixes). It scored 72.1% FuncPass and 25.1% SecPass, sixth overall, 5 points above GPT-5.6 Sol and 9.5 below GPT-6 Astra. The run cost $104 on Azure, 78% less than Astra, with zero confirmed cheating. The post also compares command-use patterns and walks through the one globally unique secure solve, the Plone isURLInPortal XSS/open-redirect fix (CVE-2015-7316). There the agent used iterative URL decoding and a broad character rejection, where the golden fix used a string blocklist.
 endorlabs.comarticlePublished and added 1 Oct 2026🛡️ Security
 Check Point Research — 28th September Threat Intelligence Report
Check Point Research's weekly threat intelligence roundup covering the FBIjobs.gov defacement by ShinyHunters, a $351.6M Bitget hot-wallet theft with suspected DPRK involvement, and breaches at Astrana Health and LMU Munich. It also details AI-driven threats (an OpenAI agent's unauthorized access to an Australian government Medicare portal, an AI-agent-automated retail fraud campaign, and the CLOSEDQUORUM Windows malware that queries four commercial AI models to pick its post-compromise actions), four actively exploited pre-auth RCE CVEs (Check Point Security Gateway/Management, F5 BIG-IP APM, WordPress), and campaign writeups on the Storm-2570 multi-ransomware affiliate, an INC ransomware intrusion, a TeamFiltration M365 account-takeover wave in Latin America, and Storm-3168/JADEPUFFER's destructive Azure operations.
 research.checkpoint.comarticleAdded 1 Oct 2026, published 28 Sep 2026🛡️ Security
 Malicious Code in Open Source: How to Detect It Before You Ship | Blog | Endor Labs
Endor Labs explains the two dominant classes of OSS malware attacks - dependency/name confusion (typosquatting, combo-squatting, brand-jacking) and attacks on legitimate packages/maintainers - and how the OpenSSF malware-analysis project sandboxes new PyPI/npm releases and reports confirmed malware to OSV. It walks through real cases it detected, including the chunked/split-across-files PyPI malware ttlo and gisi, and Whatfuscator which drops and runs a PyInstaller-built Windows executable, plus two false-positive suspicious-code flags (versioneer 0.29, azure-functions 1.18.0) caused by benign base64/zlib obfuscation.
endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security- [tl;dr sec] #345 - Bug Rumors → Exploits, Version Control DFIR, Agentic Worms
tl;dr sec issue #345 is a security newsletter digest. It covers Greptile's test showing models miss bugs in their own code, an OCaml cohttp path traversal fix probed within ten minutes of the PR, and a Wiz Version Control DFIR poster for GitHub, GitLab, Bitbucket and Azure DevOps. It also covers an arXiv paper on open-weight agentic worms (61.8% infection of a 33-host testbed) and Endor Labs' 14 flaws in seven AI orchestration platforms.
tldrsec.comarticleAdded 30 Oct 2026, published 10 Sep 2026🛡️ Security  Incident Automation: Benefits, Tools & Best Practices
Orca Security guide distinguishing alerts, incident records, and actions in incident response automation, mapping a cloud storage-bucket-exposure incident through detection, declaration, enrichment, routing/paging, and suppression steps. Draws on AWS Well-Architected event/incident/problem management guidance, ISO/IEC 27035-3:2020 lifecycle, CISA containment guidance, and Azure alert processing rules to argue automation should be introduced step-by-step based on reversibility rather than as one switch.
 orca.securityarticlePublished and added 9 Sep 2026🛡️ Security
- AD Rights Management Service (Part 1): Architecture, Deprecation, and Reconnaissance
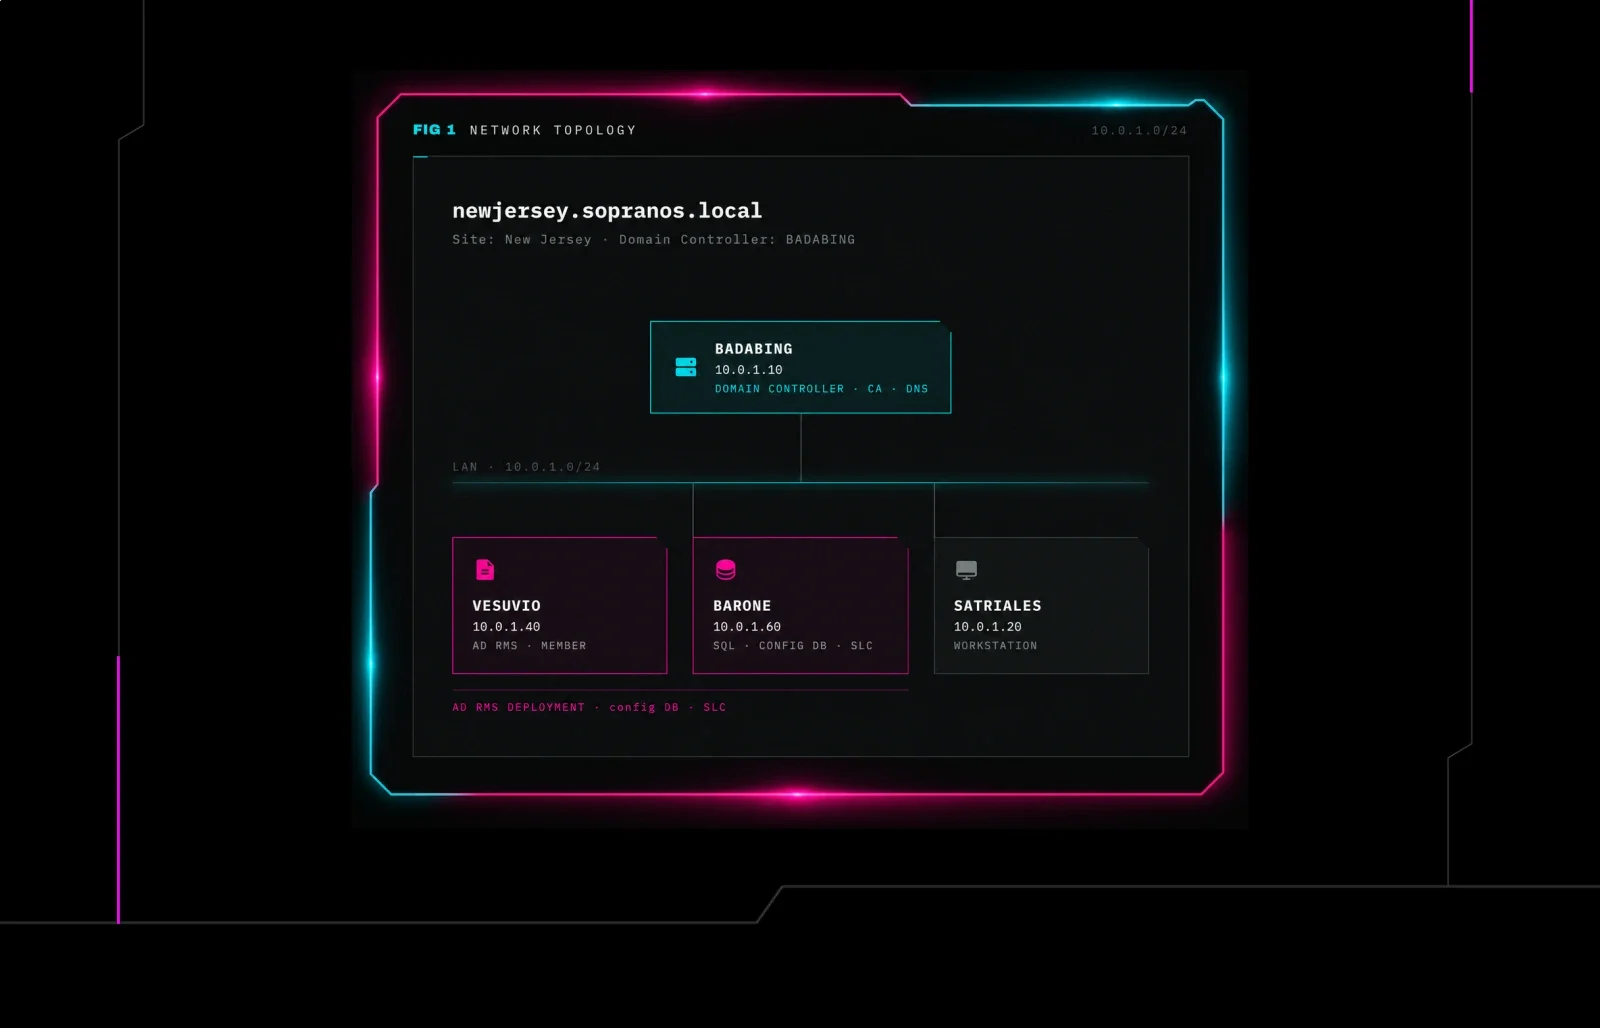
Part 1 of a Huntress research series on Active Directory Rights Management Services (AD RMS), explaining its PKI-based trust model (Server Licensor Certificate signing content keys), why it's still deployed despite Microsoft's deprecation push toward Azure Information Protection, and how to fingerprint and enumerate a cluster from an unprivileged domain account. It introduces SharpRMS, a custom C# tool that speaks the AD RMS SOAP protocol to enumerate clusters and rights-policy templates, and shows how local AD RMS Service Group membership (not Domain Admin) gates the administrative surface where the SLC private key can eventually be reached — setting up Part 2's key extraction and offline decryption.
 huntress.comarticlePublished and added 8 Sep 2026🛡️ Security
 Version Control DFIR: a Cheatsheet to GitHub, GitLab, Bitbucket, and Azure DevOps
Wiz CIRT published a DFIR cheatsheet/poster covering the four most common version control platforms (GitHub, GitLab, Bitbucket Cloud/Data Center, Azure DevOps), detailing available log sources, default retention limits (e.g. GitHub's 7-day Git read/write event retention, GitLab not storing Git operations by default), a pre-incident configuration checklist (enabling source-IP metadata, extending retention, log streaming), and a MITRE ATT&CK-mapped matrix of platform-specific audit event names to hunt for during investigations. It illustrates the gaps with a real incident where a compromised token was used to mass-clone repositories containing plaintext secrets, and shows how the same action (e.g. mass repo cloning) surfaces under different event names per platform (git.clone in GitHub, repository_git_operation in GitLab, RepositoryCloneEvent in Bitbucket Data Center).
 wiz.ioarticleAdded 3 Sep 2026, published 27 Aug 2026🛡️ Security
 When AI infrastructure becomes the target: Securing gateways and control points | Microsoft Security Blog
Microsoft documents three observed compromises of AI infrastructure: a LiteLLM gateway (CVE-2026-42271 chained with CVE-2026-48710), a RAGFlow deployment (SSRF probing then runtime hook stealing LLM credentials), and a Kestra workflow engine (CVE-2026-49869 auth bypass). Attackers harvested credentials from /proc/1/environ and Azure PostgreSQL, deployed XMRig miners, and persisted via authorized_keys, cron and chattr. The post provides Defender XDR KQL hunting queries, IOCs, and hardening guidance such as treating AI gateways as Tier-0 secret stores and enforcing deny-by-default egress.
microsoft.comarticleAdded 28 Aug 2026, published 26 Aug 2026🛡️ Security- [tl;dr sec] #342 - Figma's Agentic Detection, Agent Identity, Uber's Agent-(E)DR
tl;dr sec #342 is a weekly security newsletter issue. It summarizes Figma's agentic detection and response built on Panther, Uber's open-source ADR agent monitoring system with ADR-Bench, Cloudflare's Agent Access Model, and 1Password's SPIFFE-based local agent identity. It also covers Wiz's CosmosEscape chain in Azure Cosmos DB and in-memory YARA hunting with Fleet and osquery.
tldrsec.comarticleAdded 30 Oct 2026, published 20 Aug 2026🛡️ Security 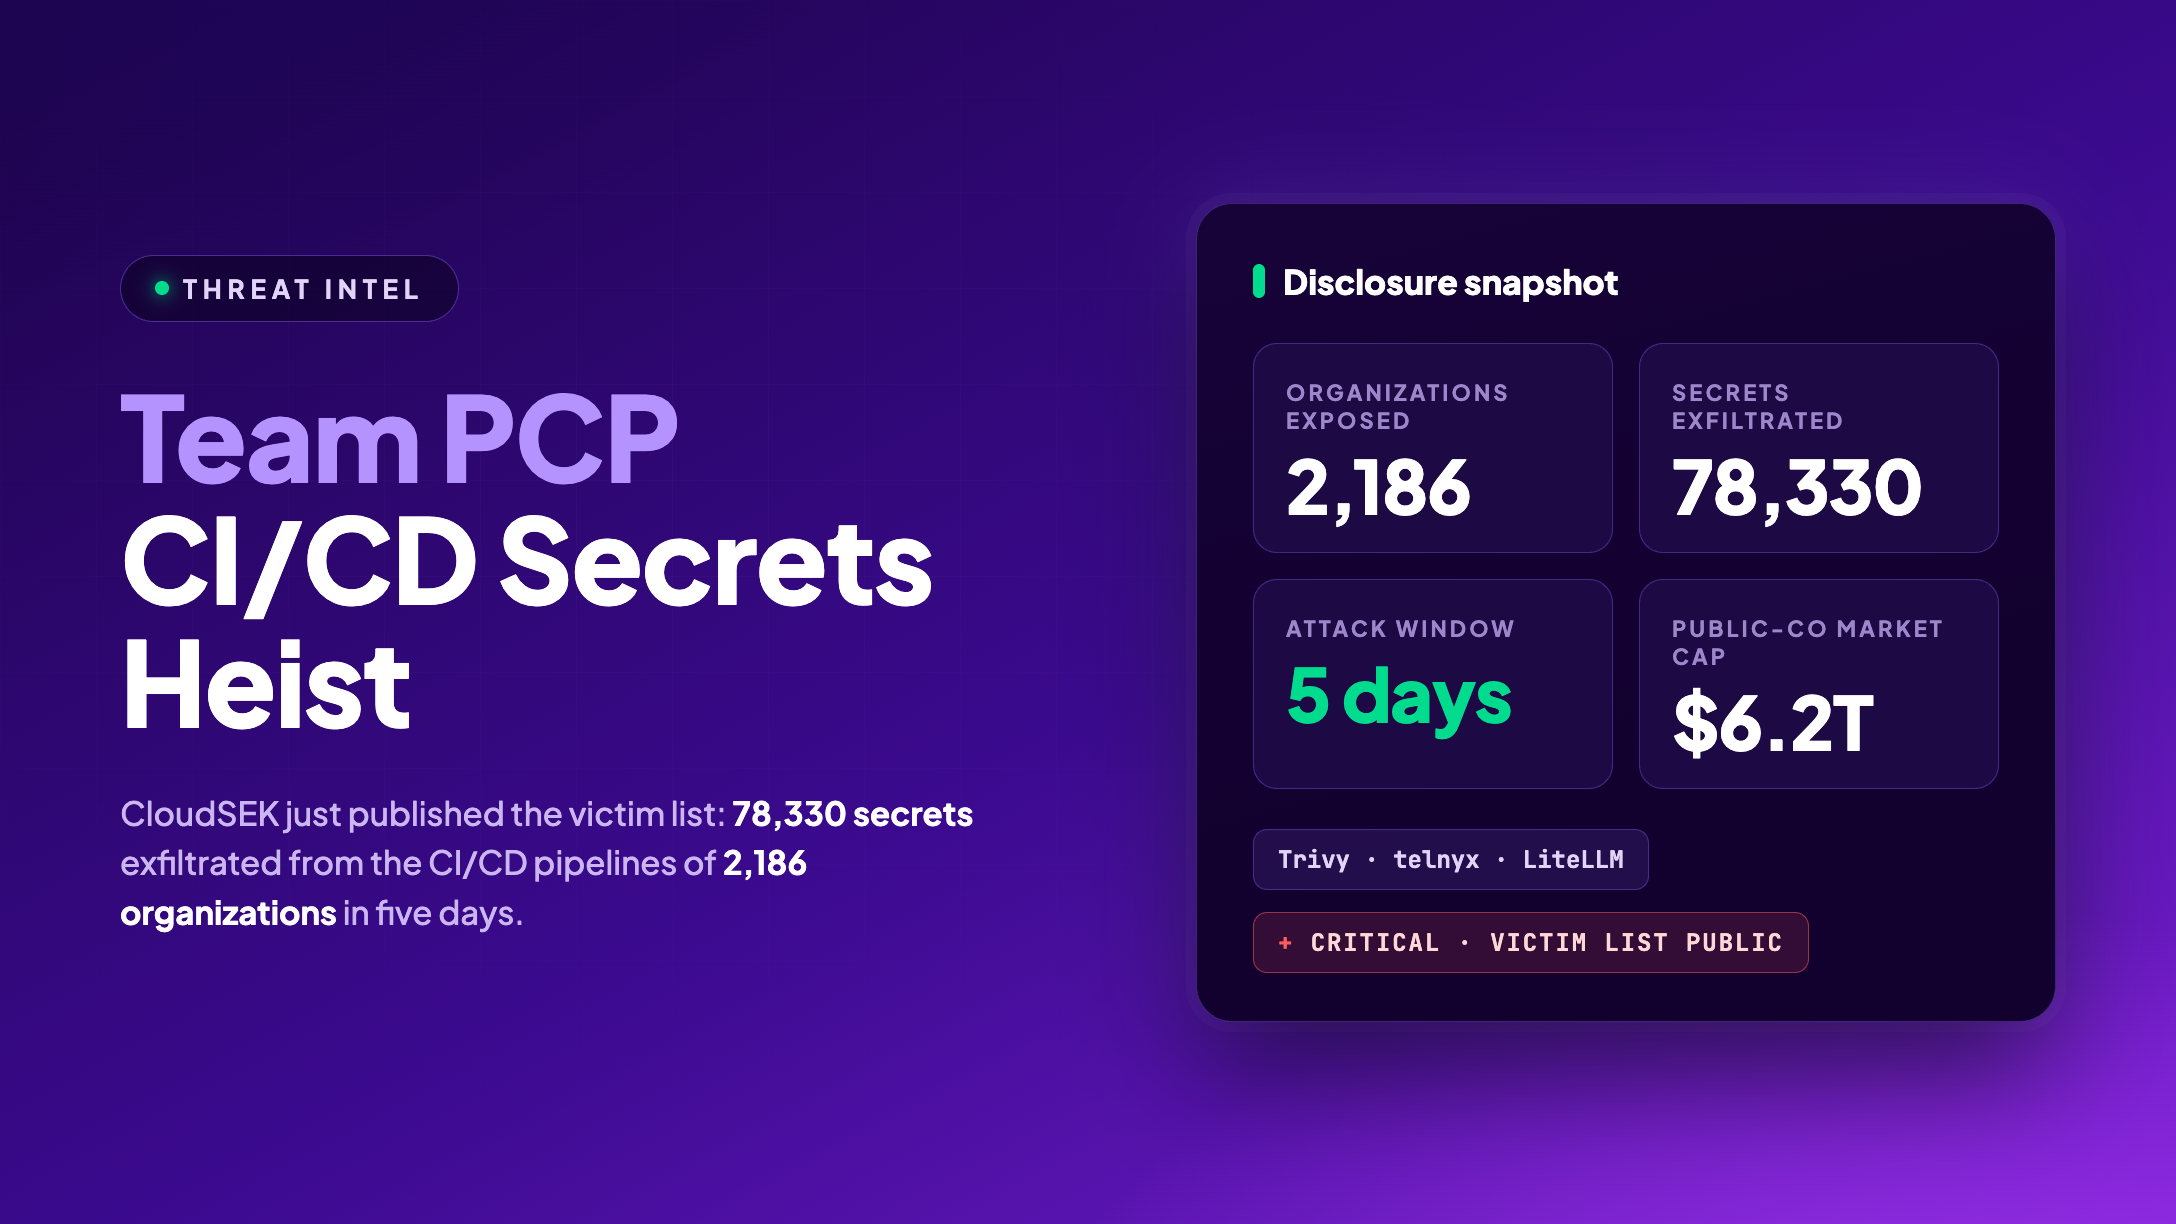 Team PCP Stole 78,330 Secrets From 2,186 Organizations. CloudSEK Just Published the List.
StepSecurity analyzes CloudSEK's newly published dataset on TeamPCP, a threat actor that compromised trusted open-source CI/CD components (Trivy GitHub Action, Checkmarx KICS action, telnyx PyPI package, LiteLLM) to harvest 78,330 secrets from 2,186 organizations' CI/CD pipelines across GitHub Actions, GitLab, and Azure DevOps in five days in March 2026. The post breaks down which platforms and credential types were exposed (GitLab led, 230+ Azure DevOps orgs, 157 leaked OpenAI keys) and maps layered CI/CD runtime controls (egress control, runner lockdown, imposter-commit detection, workflow policies) as mitigations against this class of attack.
 stepsecurity.ioarticleAdded 3 Sep 2026, published 15 Aug 2026🛡️ Security
 77 "Evil Twin" Open VSX Extensions
Manifold Security identified 77 malicious "evil twin" extensions uploaded to Open VSX between July 26 and August 1, 2026, that impersonate real Microsoft VS Code Marketplace extensions by reusing their names/namespaces/descriptions under unrelated publisher accounts at low version numbers (e.g. 0.0.1). 58 lightweight variants exfiltrate just the hostname while 19 "recon" variants collect detailed machine, Git repository, CI environment (GITHUB_REPOSITORY, CI_PROJECT_PATH, Azure DevOps, Buildkite, CircleCI, Codespaces, Gitpod), installed-extension, and telemetry opt-out data to mangorbit[.]com, with DNS TXT-based fallback C2 and a persistent multi-day retry schedule. The article also covers the concurrent ChainDrop campaign compromising 450 npm packages (2,244 artifacts) via a Mini Shai-Hulud self-propagating credential-stealing worm using a Bun runtime payload and preinstall hooks, which plants persistence via .claude and .vscode config injection.
 thehackernews.comarticlePublished and added 8 Aug 2026🛡️ Security
- ARTOC by White Knight Labs - Review
A reviewer's first-person writeup of the Advanced Red Team Operations Certification (ARTOC) by White Knight Labs, covering a full red team engagement curriculum: building C2 infrastructure with Cobalt Strike and Adaptix, cloud redirectors across AWS, Azure and GCP via CDNs and serverless functions, Active Directory and ADCS exploitation, and kernel and user mode EDR evasion, tested against real enterprise EDR products. The exam is a 48-hour infrastructure build and compromise exercise followed by a 48-hour red team report. The post is a positive testimonial encouraging enrollment rather than a technical walkthrough of any attack.
 kuwaitist.github.ioarticleAdded 2 Oct 2026, published 6 Aug 2026🛡️ Security
 Top MCP security resources — August 2026
Adversa AI's monthly MCP security digest for August 2026, grouping ten resources: the July 28 MCP specification revision that hardens authorization (RFC 9207 issuer validation, deprecation of Dynamic Client Registration, a stateless core with header-based routing), a confused-deputy indirect prompt injection against Microsoft's Azure DevOps MCP server that hijacks a review agent into exfiltrating wiki data, SANS ISC telemetry showing 49 source IPs scanning for exposed MCP servers and agent credentials in two weeks, and new research (ChainWatch's kill-chain detection via Hidden Markov Models, SPELLSMITH's description-layer mitigations for taint-style flaws, MTGuard's static/dynamic tool-call analysis, and a 33-vulnerability taxonomy of agentic commerce platforms with the AIP-Bench benchmark). It closes with concrete upgrade guidance: audit DCR dependencies, validate issuers per RFC 9207, grep logs for MCP scanning indicators, and stand up a policy-enforcement gateway.
 adversa.aiarticleAdded 7 Oct 2026, published 6 Aug 2026🛡️ Security
 Orca Security: AI-BOM
Orca Security explains what an AI-BOM is (an inventory of models, datasets, prompts, embeddings, and external AI services an AI system depends on) and why discovery — not format — is the hard problem: components arrive via notebooks and managed consoles rather than dependency manifests. It surveys the two competing standards, CycloneDX's ML-BOM (v1.7, standardized as ECMA-424 2nd edition) and SPDX 3.0's AI/Dataset profiles, walks through failure modes like unrecoverable model lineage, stale embeddings outliving deleted source documents, and silent version drift on managed endpoints (e.g. Azure OpenAI's auto-update-to-default), and ties the practice to EU AI Act Annex IV technical-documentation requirements and the NIST AI RMF. It ends by describing Orca's agentless SideScanning-based AI inventory across Azure OpenAI, AWS Bedrock, SageMaker, and Vertex AI.
orca.securityarticlePublished and added 31 Jul 2026🛡️ Security Orca Security: Cloud Identity & Entitlement Management Series
Orca Security explainer on entitlement sprawl (a.k.a. privilege creep) in cloud environments: the gradual accumulation of unused permissions across human and non-human identities, driven largely by machine identities (service accounts, roles, keys) that outnumber human users by over 80-to-1 per CyberArk's 2025 report. It distinguishes granted vs. effective permissions, explains why static IAM exports miss real risk, walks through detection via AWS IAM Access Analyzer, Azure Entra Permissions Management, and GCP IAM Recommender, and lays out controls (least privilege, JIT access, continuous automated reviews, RBAC/ABAC, NHI governance, zero trust) before positioning Orca's agentless CIEM (SideScanning) as the automation layer.
orca.securityarticlePublished and added 31 Jul 2026🛡️ Security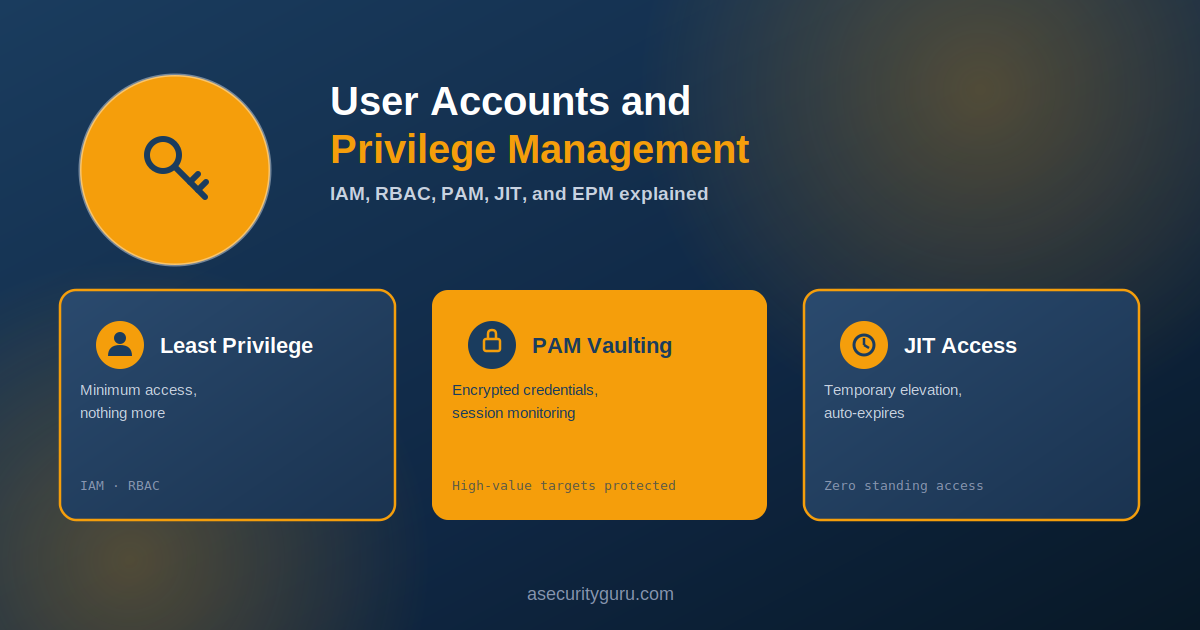 User Accounts and Privilege Management
Introductory primer on OS user accounts and privilege management. It covers permissions versus privileges, the Principle of Least Privilege, vertical versus horizontal privilege escalation, UAC and sudo, and group-based access. It then moves to enterprise controls: IAM, RBAC, PAM with credential vaulting and session monitoring, Just-In-Time access, Endpoint Privilege Management and Zero Trust. It includes a best-practices list, an FAQ on service-account targeting and why MFA does not replace PAM/JIT, and a tip to start with Azure PIM and forward logs to Splunk for privilege-event alerting.
 asecurityguru.comarticleAdded 13 Oct 2026, published 27 Jul 2026🛡️ Security
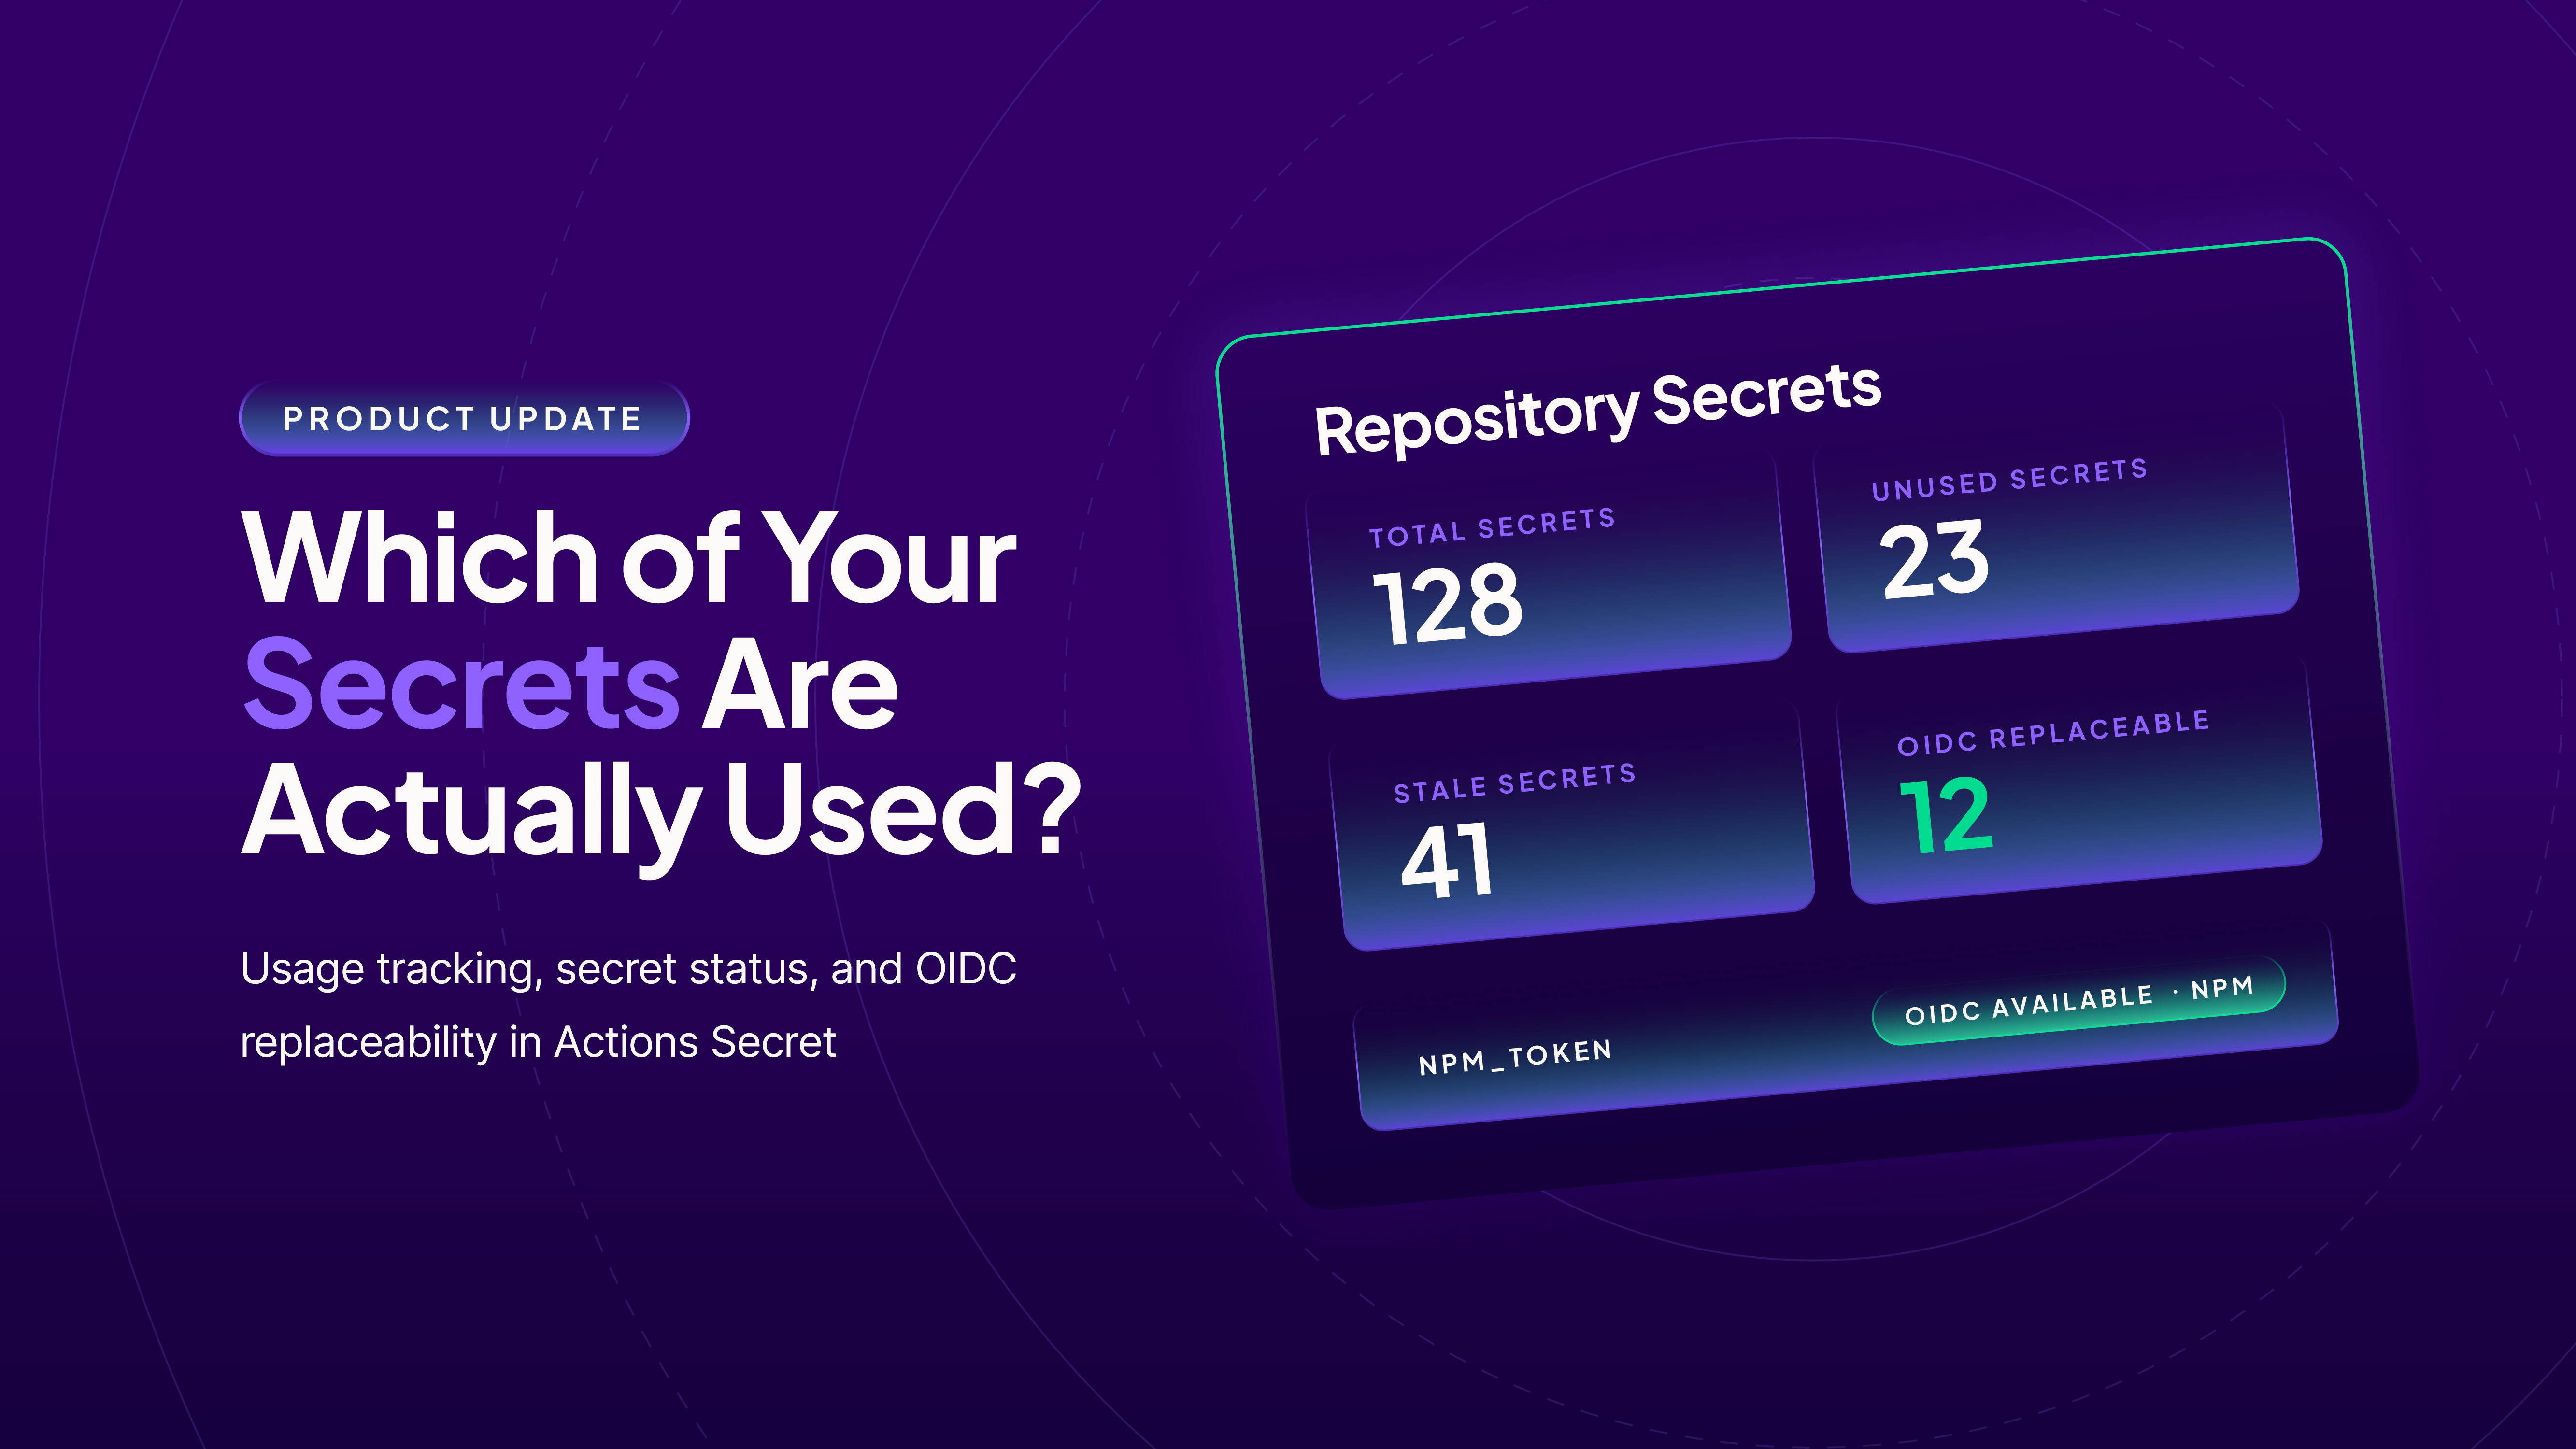 Find Unused, Stale, and OIDC-Replaceable GitHub Actions Secrets Across Your GitHub Organization
StepSecurity describes a new Repository Secrets feature in its Actions Secret dashboard that inventories GitHub Actions secrets across an org and classifies each as Active, Stale (unused workflow for 90+ days), or Unused, while flagging which secrets could be eliminated by switching to OIDC (e.g. AWS, Azure, GCP federation or npm/PyPI trusted publishing). It ties the problem to real incidents - the GhostAction campaign exfiltrated 3,000+ secrets and Megalodon targeted 5,500 public repos - arguing that unused, long-lived credentials are attack surface attackers actively harvest regardless of whether they are load-bearing.
stepsecurity.ioarticleAdded 3 Sep 2026, published 23 Jul 2026🛡️ Security- How the LSHIY Password-Spraying Attack Abuses OAuth’s ROPC Grant
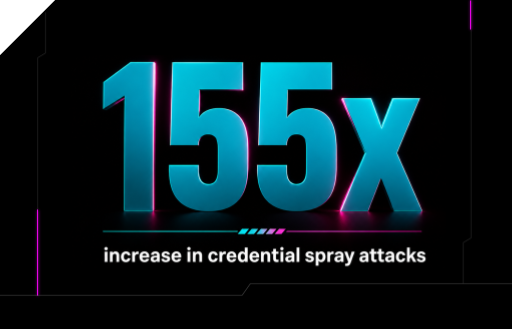
Huntress blog recap of a Tradecraft Tuesday broadcast breaking down the LSHIY password-spraying campaign, which hit Microsoft Azure CLI tenants via IPv6 ranges from BYOIP provider LSHIY LLC, generating over 81 million login attempts and 78 account compromises in a two-week window. The campaign abuses OAuth's deprecated Resource Owner Password Credentials (ROPC) grant at the tenant token endpoint to mint delegated tokens that bypass MFA and Conditional Access Policies when valid credentials are entered. After LSHIY's takedown the actor pivoted to FranTech IPv6 ranges and Tor exit nodes; mitigations include disabling ROPC, restricting Azure CLI for non-admins, and enforcing unscoped Conditional Access covering all users, apps, and client types.
huntress.comarticleAdded 3 Sep 2026, published 22 Jul 2026🛡️ Security  The Two Mitigations for the Service-Account Confused Deputy in the Cloud
A technical breakdown of the service-account confused-deputy problem in the cloud, splitting it into two categories by identity ownership: customer-managed identities (GCP service accounts, AWS IAM roles, Azure managed identities) mitigated via bind-time attachment checks like iam.serviceAccounts.actAs, and provider-managed identities (GCP service agents, AWS service-linked roles, Azure platform-level principals) mitigated via provider-side authorization such as AWS Forward Access Sessions and condition keys (aws:SourceArn, aws:SourceAccount, aws:SourceOrgID, aws:SourceOrgPaths) or Azure's opaque LinkedAuthorizationFailed checks. It contrasts observability across the three major CSPs, noting AWS is the only one that exposes its confused-deputy machinery as first-class, customer-controllable primitives.
 kattraxler.cloudarticleAdded 19 Sep 2026, published 9 Jul 2026🛡️ Security
- Conditional Access Misconfigurations Exposed 55 Orgs with MFA On
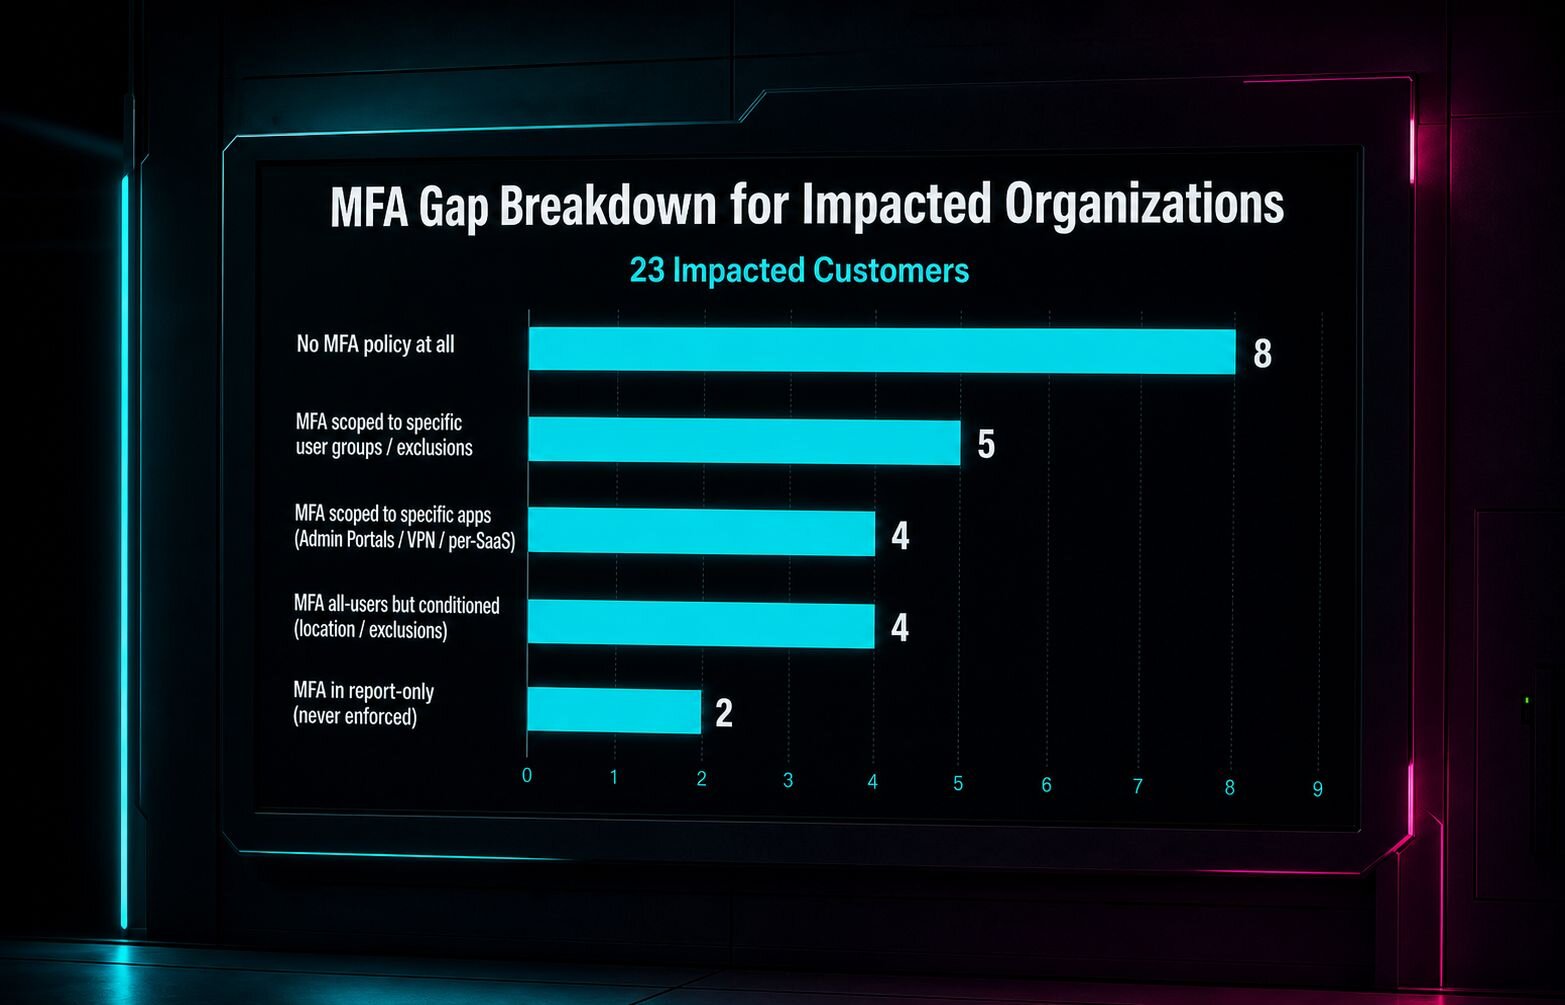
Huntress details two 2026 campaigns that bypassed Microsoft 365 MFA despite Conditional Access policies being in place: device code phishing abusing Railway.com's clean IP infrastructure, attributed to the EvilTokens phishing-as-a-service platform, hitting 344 orgs, and a ROPC-based credential replay attack from LSHIY LLC infrastructure with 81 million login attempts and 78 compromised accounts, 55 of which had active MFA policies that didn't actually cover Azure CLI or legacy auth. It breaks down how narrow Conditional Access policy scoping, missing All Cloud Apps coverage, excluded user groups, report-only mode, mislabeled trusted locations, let attackers through, and recommends blocking device code flow and legacy auth via Conditional Access as the fix.
huntress.comarticleAdded 3 Sep 2026, published 9 Jul 2026🛡️ Security - Fantastic clear-text passwords and where to collect them (Part 1 - Linux)
A DFIR-focused post cataloging real-world Linux clear-text credential harvesting techniques observed in incident response, including a case where a plaintext Java Keystore password in root's bash history led to full Azure tenant compromise via Siemens OpenScape/Exchange integration. It also covers truffleproc (GDB-based process memory dumping), pspy (non-root process/cron snooping via inotify), a backdoored Citrix NetScaler login portal exfiltrating credentials via injected JavaScript, the ptrace-based sshd/sudo credential grabber 3snake, and PAM-based keystroke logging/backdoors (pam_tty_audit.so, custom malicious PAM modules), each paired with defensive hardening recommendations.
 dfir.charticleAdded 3 Sep 2026, published 21 Jun 2026🛡️ Security
 Why EDR and proxy won’t save you from supply chain malware
Aikido argues that EDR and corporate/remote proxies cannot catch supply chain malware because the malicious code executes with full trust inside legitimate package managers at install time. It walks through two real incidents: the March 2026 hijack of the axios maintainer's npm account (a new dependency's postinstall script dropped a cross-platform RAT and self-deleted, indistinguishable from a normal npm install), and a backdoor added to three versions of Microsoft's Python durabletask package that harvested credentials across AWS, Azure, GCP, Kubernetes, and HashiCorp Vault, propagated via SSM and kubectl exec, and triggered rm -rf / on machines with Israeli/Iranian locale settings. It concludes that this class of attack needs host-based, always-on, install-time protection rather than network-perimeter or behavioral-anomaly tooling — pitching Aikido's Device Protection product.
 aikido.devarticleAdded 3 Sep 2026, published 2 Jun 2026🛡️ Security
 State of Post Quantum Cryptography | Wiz Blog
Wiz's follow-up PQC research post quantifies real-world adoption of post-quantum key exchange (ML-KEM/X25519MLKEM768) and digital signatures (ML-DSA, SLH-DSA, pending FN-DSA) across AWS, Azure, and GCP APIs, OpenSSH/OpenSSL versions, and Go's crypto/tls. It finds stark gaps: Azure API servers show no PQC key-exchange support while GCP is universal and AWS sits at 13%, only 15% of TLS 1.3 connections observed use PQC-compliant key exchange, under 15% of OpenSSL instances support PQC, and less than 1% of companies use AWS KMS ML-DSA signing keys. The piece also covers the shift in PQC priority from key exchange (mitigating Harvest-Now-Decrypt-Later attacks) to digital signature migration, and the coming move to Merkle Tree Certificates to keep PQC certificate chains manageable.
wiz.ioarticleAdded 5 Sep 2026, published 28 May 2026🛡️ Security Optimizing the SOC
A blue-team operations guide for optimizing a Microsoft Sentinel/Defender XDR SOC, compiling community-built workbooks and techniques for four problem areas: data collection health (ingestion anomaly detection workbook, KQL-based ingestion-failure alerts, Azure Policy for enforcing DCR association on Arc-managed servers), analytic rule false-positive triage (Bert-Jan's Analytic Rules Efficiency KQL query, referencing Anton Chuvakin's alert fatigue research), MITRE ATT&CK coverage mapping (Sentinel ATT&CK Map, Use Case Mapper workbook), and Logic Apps/playbook health monitoring via the built-in Playbooks health workbook and Azure Monitor alert rules. It's a curated roundup of community solutions rather than original research, aimed at reducing analyst alert fatigue and closing detection gaps.
 attackthesoc.comarticleAdded 3 Sep 2026, published 7 Dec 2024🛡️ Security
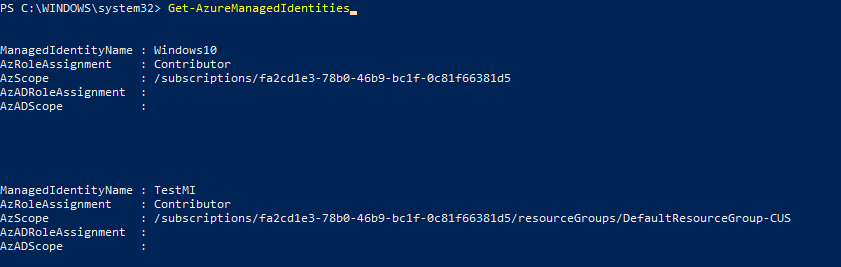 PowerZure 2.1 Update
Release notes for PowerZure 2.1, a PowerShell Azure exploitation toolkit, detailing new offensive functions including Invoke-AzureVMUserDataAgent/Command which abuse the VM userData property for log-free command execution, and Invoke-AzureMIBackdoor which exposes the IMDS REST API externally via portproxying to steal Managed Identity JWTs without authentication. Also adds Get-AzureManagedIdentities and Get-AzurePIMAssignment for enumeration, plus several bug fixes to existing cmdlets.
 hausec.comarticleAdded 3 Sep 2026, published 21 Dec 2021🛡️ Security