- Lonnie VanZandt (@lonniev) on X
Secure Courier is a consent flow in Tollbooth DPYC, a monetization network for paid MCP services, that lets an AI agent act for a Nostr npub without holding the user's nsec. The service sends a signed, sealed direct message over Nostr relays, the user replies with a signed approval and an expiry, and the service issues its own encrypted grant. Lonnie VanZandt presents it as an alternative to central identity providers and CIBA. The thread gives no audit results.
 x.comthreadAdded 1 Nov 2026🧠 AI
- ERC-8481: Agent Pre-Sign Risk Report
ERC-8481 is a draft Ethereum standard for the report a risk source returns about one unsigned transaction, EIP-712 request or x402 requirement. The report is bound to the request by a digest and EIP-712 signed by an ERC-8004 identity. It has five typed finding groups (tokens, approvals, addresses, payments, texts), each marked read or not read, and carries no score or verdict. The author's service toll is the only implementation; three design questions are open.
 ethereum-magicians.orgthreadAdded 2 Nov 2026, published 31 Oct 2026🛡️ Security
 Pre-ERC: Agent Pre-Sign Risk Report
 is an Ethereum Magicians draft for a signed, typed report that a risk source returns about one unsigned agent transaction. The report is bound to the request by a digest and signed with EIP-712 by an ERC-8004 identity. Findings cover tokens, approvals, addresses, x402 payments and texts, each marked read or not read, with no score or verdict. The toll service runs it live on Robinhood Chain.
ethereum-magicians.orgthreadPublished and added 31 Oct 2026🧠 AI- Dark Web Intelligence (@DailyDarkWeb) on X
CVE-2026-102764 is an unauthenticated RCE in BeyondTrust Remote Support, already exploited and in CISA KEV. Rapid7 published an analysis and opened a Metasploit pull request on 30 October 2026, showing code execution on version 24.1.2 via a forged "local" message origin, the native file-transfer service and a PHP file written to the web root. BT26-05 (CVSS 4.0 9.3) is fixed by patch BT26-05-RS; SaaS was patched by 9 October.
x.comthreadAdded 1 Nov 2026, published 31 Oct 2026🛡️ Security  ERC draft: Independent Simulation Result for (STVA)
ERC draft "Independent Simulation Result" (STVA) defines a canonical, content-addressed SimulationResult (success, gasUsed, returnData, stateDiffHash, logsHash, snapshotId, resultHash) that any wallet, hardware device or verifier can recompute from the same VerificationPayload and state snapshot. It targets compromised-frontend and UI/calldata-mismatch attacks, and defines Basic, Standard and Strict compliance levels. Open questions are stateDiff encoding, prestate proofs and binding to capability tokens.
 ethresear.chthreadPublished and added 30 Oct 2026🛡️ Security
- Lonnie VanZandt (@lonniev) on X
Tollbooth DPYC's "Secure Courier" is a consent scheme that lets an AI agent act for a Nostr npub at a paid MCP service without holding the user's nsec. The service sends a signed, sealed Nostr direct message, the user replies signed with their nsec and sets an expiry, and the service issues its own grant. The thread contrasts this with central identity providers and CIBA, arguing a breach reaches only grants that service issued.
x.comthreadAdded 1 Nov 2026, published 30 Oct 2026🛡️ Security  Trail of Bits (@trailofbits) on X
Trail of Bits post on X summarising Binance's initial investigation into a security incident. Binance suggests a compromised DevOps engineer's laptop let an attacker reach a service container and submit unauthorized withdrawal transactions. The text says no evidence has been found of wallet private key compromise. The fetched text is truncated and gives no further detail.
x.comthreadPublished and added 30 Oct 2026🛡️ Security- aiproduck (@aiproduck) on X
Ruflo is an MIT-licensed wrapper for Claude Code and Codex that adds agent swarms, vector memory and an MCP server. The plugin install writes no files to the workspace, while npx init adds a .claude/ directory, CLAUDE.md and hooks. The post warns that mods run with the account's permissions, so users should read them first. It gives no benchmarks or architecture detail.
x.comthreadPublished and added 30 Oct 2026🧠 AI - 🚨 AI News | TestingCatalog (@testingcatalog) on X
Mistral Large 4 ("Le Chonk") is an open-weights model from Mistral, now on Hugging Face. Per Mistral's announcement quoted in the post, it ranks #1 among open models on Cognition's FrontierCode benchmark, is aimed at agentic coding and cybersecurity, and claims better reasoning efficiency and lower inference costs. The post does not give parameter counts, license or benchmark scores.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI - 🚨 AI News | TestingCatalog (@testingcatalog) on X
Nemotron 3.5 Transcribe is an open-weight, promptable NVIDIA mixture-of-experts model with 30B total and about 4B active parameters. One checkpoint does transcription in 40 languages, speaker attribution, translation, contextual prompting and audio understanding. The post says it ranked first in VoiceArena's comparison of 14 diarization plus ASR systems. The fetched text is cut off and gives no license or download details.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI - Trail of Bits (@trailofbits) on X
Trail of Bits post says it achieved remote code execution through a Brotli decoder bug in Linux lab setups: Node.js 24.22.0 with Express 5.3.0 via the standard JSON parser (x86-64 and ARM64), and Electron 41.10.7 (x86-64) with a custom decoding service. Exploitation needs a carefully matched setup and repeated attempts. A scanner by ToBScottA finds hidden copies of the decoder, including in stripped binaries.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security  Abdullah (@abdullah0094) on X
An X thread by Abdullah on GPT-6.1 Terra versus Sol in Codex. Abdullah says Terra gives twice the Codex usage of Sol and asks whether the quality drop is obvious. A reply says it is too early for a verdict, cites OpenAI's claim that Terra matches GPT-6 Astra on Agents' Last Exam, and suggests defaulting to Terra and switching to Sol with /model when it stalls.
x.comthreadPublished and added 27 Oct 2026🧠 AI- The SI Maximalist (@thesimaximalist) on X
The SI Maximalist posts on X that OpenAI says GPT-6.1 Terra matches GPT-6 Astra on Agents' Last Exam, OpenAI's test of workplace software tasks, at one tenth of the token price. The model is available in ChatGPT Work, Codex and the API. The post only relays OpenAI's claim and gives no benchmark scores, exact prices or method.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🧠 AI  Akash Rajagopal (@akashsairaja) on X
Ollama overview thread by Akash Rajagopal on X. It lists six steps: install on macOS, Linux, Windows or Docker; run `ollama run gemma4`; use the REST API on localhost:11434 (/api/chat); call it from ollama-python and ollama-js; llama.cpp as the README's supported backend; and `ollama launch claude` to connect Claude Code. Codex, OpenCode, Copilot CLI and Droid also work. The thread cites 184k GitHub stars and an MIT licence.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🧠 AI David Gutierrez | Eng (@david_x_ai) on X
Thread on two October 2026 npm compromises: @subql/common 5.8.3 (5 October), published through GitHub Actions OIDC Trusted Publishing after the attacker tampered with the publish workflow, and tensorlake 0.5.144 (8 October), published by the project's own release workflow with valid provenance for about 1 hour 40 minutes. Both ran on install and stole cloud, GitHub, Kubernetes, Vault, SSH and .env credentials; tensorlake also took AI tool and MCP config. Its payload installed a gh-token-monitor service that deletes the home directory if the stolen GitHub token is revoked, so remove it before rotating.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security Benjamin👨💻 (@Hislordship_9) on X
Thread on Forever Security's finding that a planted Markdown "Engineering Work Guidelines" file in ~/Downloads made Codex add a "project-tools" MCP server to ~/.codex/config.toml. The server ran npm install function-color, a known malicious package, and started a child session with --dangerously-bypass-approvals-and-sandbox. Codex complied in over 90% of the firm's tests; Claude Code, via a CLAUDE.md setting ANTHROPIC_BASE_URL, about half. Advice: don't start agents in Downloads, review instruction files, and diff agent config.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
Reply on X explaining a Bytecode Alliance advisory for Wasmtime's Cranelift compiler backend. A large or crafted Wasm function that generates enough SSA values overflows Cranelift's value-index representation, which packed indices into 24-bit fields. The fix widens them to 32 bits. The issue is not AArch64-specific, and the advisory names no required optimisation level. Guard pages do not reliably stop the resulting miscompilation and type confusion, so a sandbox escape can arise at compile time.
x.comthreadAdded 28 Oct 2026, published 26 Oct 2026🛡️ Security - SemiAnalysis (@SemiAnalysis_) on X
SemiAnalysis claims AMD chips running vLLM can earn up to $3 per chip-hour in profit serving the open-source Kimi K3 model, even after higher chip rental prices following Claude Code's rise. Kimi K3 has over 2.8 trillion parameters and fits AMD's 288GB per chip, while B200 cannot hold it in one server. B200 must then use tensor or pipeline parallelism over 400Gbit/s InfiniBand or Ethernet, which SemiAnalysis says is 18x slower than NVLink. The post gives no methodology.
x.comthreadAdded 26 Oct 2026, published 25 Oct 2026🧠 AI  ReignSwords (@ReignSwords) on X
A reviewer tests GenOffice, an open-source Office suite (10.7k GitHub stars), through its CLI only. Markdown to .docx took 3.8s, JSON to .xlsx took 0.9s with a live SUM formula, and .docx to PDF failed twice until Xvfb supplied a display. It has byte-preserving edits, a skill file for Claude Code and Codex, and 29 MCP tools. Downsides: a 188MB download that filled a 512MB /tmp, Electron in the PDF path, and unproven trust in tracked changes and rollback.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🧠 AI Hajrë Hyseni | AI for Business (@hajra) on X
Kimi K3.1 Pro is a new model from Moonshot AI. According to a post by hajra, Artificial Analysis ranks it 4th in the world, 3 points behind Claude Opus 5.5. The API price is down by a third, and full open weights are promised by 4 November. The post gives no benchmark breakdown, licence or architecture details.
x.comthreadPublished and added 24 Oct 2026🧠 AI Daily Vibe Casting (@vibecastingapp) on X
Daily Vibe Casting is an X thread dated 24 October 2026 that summarises ten tech news items from the previous 24 hours. The AI items are Cloudflare's model-independent agent security audit skill, Recursive SI's Apache 2.0 Flint local coding model (125+ tokens/s on an M4 Pro), Anthropic's Claude Duet preview and Claude API version 2026-10-21, which drops temperature, top_p and top_k. It also covers HeyGen Voice Turbo and Gemini in Google Maps on CarPlay.
x.comthreadAdded 24 Oct 2026, published 22 Oct 2026🧠 AI- SpyTech Ai (@RizeOnline) on X
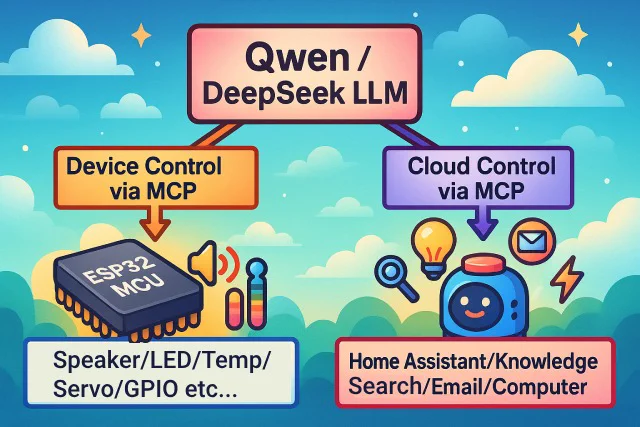
XiaoZhi ESP32 is an open-source, MIT-licensed firmware stack that turns ESP32 boards into MCP-based voice chatbots using models such as Qwen and DeepSeek. It streams Opus audio over WebSocket or MQTT + UDP through ASR, LLM and TTS, adds offline ESP-SR wake words, and uses device-side MCP to drive speakers, LEDs, servos and GPIO. It supports 138 board directories and builds with ESP-IDF 6.0.1 or newer.
x.comthreadAdded 23 Oct 2026, published 21 Oct 2026🧠 AI  VibecodersHQ (@VibeCodrHQ) on X
Post summarising Pillar Security's finding of a remote code execution flaw in OpenCode, the open-source AI coding agent. Versions 1.0.137 through 1.18.32 could run code from a remote MCP server during OAuth sign-in on Windows and WSL, with no prompt injection needed. The fix is in 1.18.33 (released 28 September). No advisory or CVE was issued, so scanners will not flag old installs. Interim advice is to remove unvetted remote MCP servers.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security SemiAnalysis (@SemiAnalysis_) on X
SemiAnalysis thread arguing that vLLM with Wide-EP and EPLB can reproduce DeepSeek's serving performance. It reports decode throughput within 6% of DeepSeek's DeepInfer release and about $39 per GPU-hour revenue at DeepSeek's off-peak pricing, at 200 P90 TPS on the AgentX workload. It explains why DeepInfer is not on InferenceX: the release supports only offline, single-turn inference. It also estimates GB300 profit at OpenRouter prices.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🧠 AI Billy Lee (@billyozno) on X
LiteLLM 1.107.0 on PyPI shipped malware in all 7 wheels, the package's second supply-chain attack this year. It steals SSH keys, cloud credentials, browser passwords, AI tool configs and API keys, and installs a backdoor that polls for commands hourly. The GitHub source is clean, so a hijacked build or publish step is suspected. PyPI quarantined the release, but Aikido says the Docker image litellm/litellm:1.107.0 was still live. Indicators are cook.pth, cook.py and sitecustomize.py in site-packages. The advice is to rotate reachable keys and pin 1.106.2.
x.comthreadAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security- Vishesh Raheja (@entropyconquers) on X
GPT Voice is a free, open-source Mac app by Vishesh Raheja that brings ChatGPT's dictation to any macOS app. A shortcut starts recording, and the transcript is pasted where the user is typing. It uses the ChatGPT Pro subscription, so it needs no API key or extra subscription. The author built it after Handy handled coding prompts poorly and they did not want to pay for Wispr Flow. The thread gives no details on local versus API transcription or latency.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🧠 AI - ︎ (@0xocdsec) on X
Post from 0xocdsec announcing a deep-dive on CVE-2026-106173 in Fortinet FortiSIEM. The flaw is an arbitrary file write in a gRPC service that leads to remote code execution. The author says this is the fourth year in a row they have researched FortiSIEM. The post itself gives no technical detail and links to the full analysis.
x.comthreadAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security - LinuxSecurity (@lnxsec) on X
A post from lnxsec on CI runners that accept outside pull requests while also holding registry credentials, cache write access, signing material or deployment tokens. It uses the Nix/Lix build-service issues to argue that host compromise and downstream artifact trust are separate risks. It lists four checks: enumerate secrets exposed to PR jobs, split untrusted runners from release runners, trim registry and binary-cache write permissions, and require independent approval for release. It links a linuxsecurity.com feature; CVE details are not in the post.
x.comthreadAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security  Bitcoin News (@BitcoinNewsCom) on X
Mark Karpelès, former Mt. Gox CEO, says he is building a low-cost device to detect hidden LTE antenna spy implants in hardware wallets such as Ledger without opening them. It emits weak radio waves and measures resonance frequencies. He plans to publish the PCB designs and specs; the project is at concept stage with a prototype expected within weeks. A linked YouTube video is not covered in the text.
x.comthreadAdded 20 Oct 2026, published 18 Oct 2026🛡️ Security 🚨 AI News | TestingCatalog (@testingcatalog) on X
A TestingCatalog X post with two Daily AI Briefs (Oct 17 and the start of Oct 16), grouped by vendor. Oct 17 items include GPT-6 Astra Pro upgrades in ChatGPT, Codex context reuse and caching, Gemini 4 Argon in AI Studio Build, the open-weight MIT-licensed DeepSeek-V4.1-Flash-1017, Claude Code Review going GA, Perplexity's open Decider v1.2 models (27B and 4B), NVIDIA's 4B looped Nemotron Labs Dory 1.0, Reflection's Apache-2.0 Beam, Cursor cloud-agent canvases and Tencent's Hy Memory 2.0. Oct 16 begins with Meta's open-weight Muse Spark Open, an 816B-total, 42B-active MoE with a 1M-token context. It gives a quick snapshot of the week's open-weight and coding-agent releases.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🧠 AI- Dark Web Intelligence (@DailyDarkWeb) on X
Post summarizing independent researcher Sammy Azdoufal's report on EnergizeLab's Eilik companion robots, which are marketed mostly to kids. Per the report, any registered user could read other families' chat transcripts through the vendor back office. An unauthenticated endpoint also lets anyone swap the robot's AI model, voice and personality (CVE-2026-105038, CVSS 9.8, PoC listed by the CNA). At the Oct 13 retest, 32 of 40 remotely testable findings were still open. The post notes that The Verge demonstrated the issue on its reporter's own toy, that vendor remediation is unverified, and that broader malicious compromise is unproven.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🛡️ Security - Rodrigo ES Porto (@RodrigoESPorto) on X
X thread reporting that Meta confirmed Muse Spark (the coding and agent model) weights are coming, with no date and no license announced. The only Muse that can currently be self-hosted is Muse Glimmer, a 30B distilled build that works with vLLM and llama.cpp. The flagship Muse Wonder and Wonder Full stay closed, and Wonder is offered on the API with 1M-token context at $4 input and $20 output per million tokens. It also notes that in CTF red-teaming Wonder Full solved 92 objectives, 71 of them through unintended system vulnerabilities, and that the ARGUS group says the 13-page model card omits test methods and raw results.
x.comthreadAdded 17 Oct 2026, published 16 Oct 2026🧠 AI  Nicholas Martin (@ndgmlondon) on X
An X post advises auditing every MCP write tool against the database role it actually runs under. A shared service key lets prompt injection trigger unapproved writes, so each agent session should get a read-only role, with a test that writes are denied. Replies note that MCP servers often inherit ambient host credentials or can escalate through a second connection pool, and suggest also testing that another tenant's rows are unreadable with the same role.
x.comthreadAdded 18 Oct 2026, published 16 Oct 2026🛡️ Security Connor (@ConnorTalksAI) on X
A tweet relaying OpenAI's announcement of GPT-Live-1.1, an update to the voice model behind ChatGPT voice mode. It reduces how often the model says "checking", adds new voices and improves accents, including new voices in French, German, Hindi, Mexican Spanish, Korean and Japanese. It is rolling out to all users in ChatGPT, Codex and "dots", with API access coming soon. The poster frames it as a response to a new xAI/SpaceXSI Grok Voice release.
x.comthreadAdded 16 Oct 2026, published 15 Oct 2026🧠 AI- P7RIM3 (@P7RIM3) on X
Tweet about an unofficial open firmware, "waved", for the Insta360 Wave conference speakerphone, written as a single Rust program with a one-script revert to stock. The linked writeup reports that stock firmware sends 35+ usage event types tagged with the serial number to ByteDance's DataFinder, routes meeting audio, transcripts and voiceprints to Insta360's cloud, and signs updates with a 512-bit RSA key. Releases up to 1.0.13.6 exposed a root telnet shell with the password 123456. It matters as a firmware teardown of a privacy-sensitive meeting-room IoT device.
x.comthreadAdded 16 Oct 2026, published 15 Oct 2026🛡️ Security  Dark Web Informer (@DarkWebInformer) on X
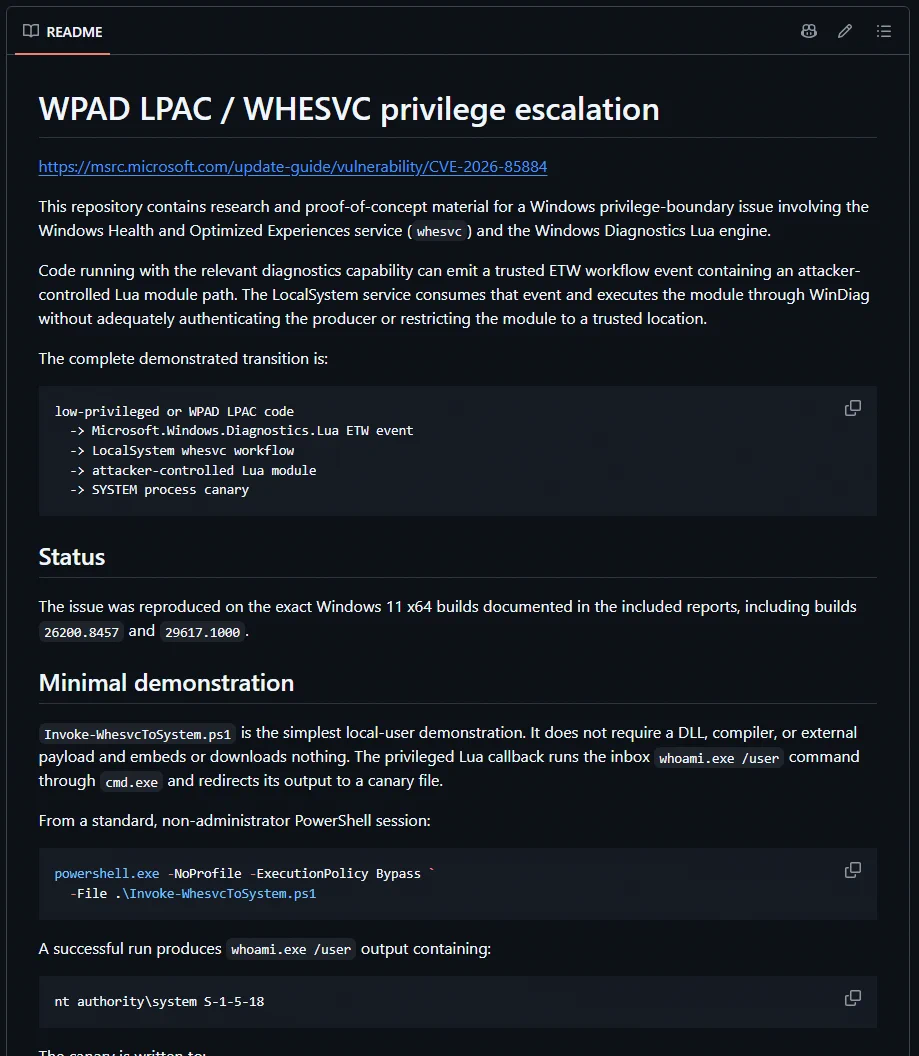
A DarkWebInformer post announces a public PoC for CVE-2026-85884, a Windows privilege escalation in the Windows Health and Optimized Experiences service. Per the post, low-privileged code with access to the Windows diagnostics workflow can trigger the flaw. The PoC is hosted in a GitHub repo by Beardhammer; the tweet text is truncated, so the exact root cause is not stated.
x.comthreadAdded 16 Oct 2026, published 14 Oct 2026🛡️ Security- Dark Web Informer (@DarkWebInformer) on X
DarkWebInformer post on a PoC for CVE-2026-85884, a Windows 11 local privilege escalation in the Windows Health and Optimized Experiences service. Low-privileged code can trigger a trusted ETW event carrying an attacker-controlled Lua module path. The LocalSystem whesvc service then runs that module through WinDiag without validating the event producer or restricting the module location. The PoC takes a standard non-admin PowerShell session to NT AUTHORITY\SYSTEM on Windows 11 x64 builds including 26200.8457 and 29617.1000.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026🛡️ Security - Dark Web Informer (@DarkWebInformer) on X
Social post announcing a PoC (hakaioffsec) for CVE-2026-82957, an SSRF in Hyperledger FireFly ≤ 1.5.0 (CVSS 8.5). Webhook subscriptions accept a user-controlled URL without validating the destination host, letting the FireFly node reach internal services, private networks, loopback and cloud metadata endpoints. The PoC creates a malicious webhook subscription, triggers a matching event and confirms the request originates from the FireFly server.
x.comthreadPublished and added 13 Oct 2026🛡️ Security  Phillip Shoemaker (@pbsIdentity) on X
Social thread reacting to a newly disclosed high-severity OAuth vulnerability in the Model Context Protocol Python SDK, where a malicious MCP server could manipulate the authorization flow and steal credentials used by an agent. The author uses it to argue that delegated agent authority needs provenance (who granted it, to which agent, for which service and resource, whether it is transferable or replayable, and when it expires) and that machine-to-machine trust must be auditable by humans. Gives no CVE ID or technical exploit detail.
x.comthreadAdded 13 Oct 2026, published 12 Oct 2026🛡️ Security- [Pre-ERC Discussion] Agent Service Order Amendments
Ethereum Magicians pre-ERC discussion proposing a signed, EIP-712 amendment object for changing an existing agent service order (scope, acceptance criteria, price increase, deadline extension) without losing the prior agreement or implicitly authorizing extra spending. It defines Amendment and Terms structs with revision, terms-hash and nonce checks, stale-revision rejection, and a freeze on amendments once work is submitted. It also asks whether this should be a standalone ERC or a profile of ERC-8001, and compares it to ERC-8414 (task tenders) and ERC-8412 (preregistered acceptance criteria). A local JavaScript state-machine experiment exists, and the Finch Agent integration is the motivating use case.
ethereum-magicians.orgthreadPublished and added 10 Oct 2026🧠 AI - Adam Shepherd (@EntryStateGod) on X
Social post announcing Qwen's open-weights release of Qwen-Image-2.1-Turbo, an accelerated checkpoint of Qwen-Image-2.1 on the same 7B visual generation architecture. It generates and edits images in 8 denoising steps, against 40 in the base model's sample code, with 2K output. Qwen claims the fewer steps do not reduce quality. The license is non-commercial, which limits production use.
x.comthreadPublished and added 9 Oct 2026🧠 AI  RJ (@RJiOSDEV) on X
A tweet reporting JetBrains' Oct 8 release of Mellum2.1, an open-weights coding model under Apache 2.0. It has 12B total parameters with 2.5B active, which implies a mixture-of-experts design. JetBrains says the model can explore repos, edit files and check changes, so it works as a coding agent. The tweet asks whether developers would self-host a coding agent. The model matters because it is a small-active-parameter, permissively licensed option for running coding agents on private infrastructure.
x.comthreadPublished and added 9 Oct 2026🧠 AI- Ned Peterson (@NedPeterson99) on X
A post summarizing a joint FBI and six-country advisory on actors tied to Integrity Technology Group (the sanctioned Chinese firm linked to Flax Typhoon and the Raptor Train botnet). They password-sprayed Microsoft 365 and Exchange accounts over EWS, OWA, ActiveSync and PowerShell with EBurst. They then drained mailboxes with a PHP bot over Exchange Web Services and an office-cli utility using stored client ID, tenant ID and secret values, and exposed the stolen email to third parties through a web app, in some cases restricted to Xiamen IP addresses. Victims were in government, law enforcement, healthcare and religious organizations across Southeast Asia, Africa and North America, with activity since at least January 2021. Defensive takeaways: enforce MFA on every legacy path, retire basic auth and EWS, audit OAuth apps and service principals with mail-read rights, and alert on bulk mailbox pulls.
x.comthreadAdded 11 Oct 2026, published 9 Oct 2026🛡️ Security  Dark Web Informer (@DarkWebInformer) on X
A security researcher released a PoC (on GitHub, user kolmteistov) and a patch for two critical takeover vulnerabilities in GoBalance, the Bitcoin balance-checking software widely used by Tor darknet market and forum onion services. One of the flaws allows recovery of a GoBalance onion service's master identity key from a single public key, enabling full service takeover; the vulnerabilities were reportedly exploited in real attacks against the Dread forum and Omega Darknet Market.
x.comthreadPublished and added 8 Oct 2026🛡️ Security- Dark Web Intelligence (@DailyDarkWeb) on X
A Twitter/X post digests joint advisory AA26-281A from FBI, CISA, NSA and allied agencies (UK, Australia, Canada, Japan, New Zealand, Spain) on China-based Integrity Technology Group enabling threat actors, tracked elsewhere as Flax Typhoon, Ethereal Panda and Red Juliett, to target US critical infrastructure, government, healthcare, education and law enforcement networks worldwide. The actors chain open-source scanners, large botnets, XSS, password spraying against Microsoft Exchange, VPN persistence and credential-harvesting scripts. CISA added five exploited CVEs (ISC BIND, Apache Struts, ProFTPD, ONLYOFFICE Docs, Strapi) to its KEV catalog with an Oct 11 federal remediation deadline, and STIX IOCs accompany the advisory.
x.comthreadPublished and added 8 Oct 2026🛡️ Security - Dark Web Informer (@DarkWebInformer) on X
Post announcing a PoC and security patch for two critical GoBalance (Tor onion service load balancer) takeover flaws, reportedly used in attacks on the Dread and Omega darknet markets. The first flaw reuses or mishandles the nonce in blinded signing, so a single public descriptor lets an attacker recover the onion service's master identity key. The second accepts forged instance descriptors without signature and identity-binding checks, which allows full frontend traffic hijacking. The linked package includes a PoC for both paths, a patched source tree, regression tests and a unified patch. It affects master at commit bb1b0f3.
x.comthreadAdded 9 Oct 2026, published 8 Oct 2026🛡️ Security - DevopsCube (@devopscube) on X
A tweet highlighting Steampipe, an open-source tool that lets practitioners query cloud infrastructure, Kubernetes, and other services using SQL instead of jumping between consoles or writing ad-hoc scripts. It calls out concrete security/ops use cases such as finding publicly accessible storage buckets, resources missing required labels, and Kubernetes namespaces without NetworkPolicies, and links to a longer tutorial on devopscube.com. The author frames it as a quick investigation layer on top of live cloud data, not a CSPM/AWS Config replacement.
x.comthreadAdded 8 Oct 2026, published 7 Oct 2026🛡️ Security - Randy Northrup (@starsoldier420) on X
Muse Spark Code is an open-source coding agent wrapping Meta's Muse Spark model, exposed as an ACP (Agent Client Protocol) agent so any ACP-compatible client, including Neovim, can drive it. It runs either through a Muse subscription via the Muse Code CLI or with a direct Model API key, and its latest release adds local dev-server browser checks and a Muse Gadgets skill for ESP32 hardware work; it's MIT-licensed with no telemetry.
x.comthreadPublished and added 5 Oct 2026🧠 AI - Meer Tarbani - Growth & Engineering (@MeerTarbani) on X
Sidekick is an open-source macOS plugin for Claude Code that lets you define a one-sentence persona (e.g. "a blunt senior Rust dev") and drive a coding session hands-free by voice: it listens via Apple's on-device speech recognition, speaks answers with macOS voices, and lets you interrupt it mid-reply or say "stop" to cancel a turn. It also surfaces Claude's multiple-choice decisions as spoken questions, matching answers like "the second one" against an echo-filtered transcript so the assistant doesn't hear and respond to its own voice. Implementation is a ~500-line TypeScript Claude Code hooks module plus a 90-line Swift speech listener, runs fully local with zero servers and zero telemetry, and installs via the `claude plugin marketplace`/`claude plugin install` commands.
x.comthreadPublished and added 4 Oct 2026🧠 AI - Sahil Verma (@sahilvermaai) on X
Aleph Alpha released Kolibri, a 78B-parameter open-weight mixture-of-experts model with only 3.46B active parameters per token, a 1M token context window, and Apache 2.0 licensing with full weights on Hugging Face. The model was trained on German and Finnish infrastructure, positioning it as a European-built alternative to US/Chinese open-weight releases.
x.comthreadPublished and added 4 Oct 2026🧠 AI  Rajashekar Sudireddy (@raja_sudireddy) on X
A tweet thread recapping Nate Herk's 18-concept guide to running OpenAI's Codex as a non-coder "AI operating system," organized around four pillars: a place to work (projects, AGENTS.md, the agent loop), a place to run it (local vs cloud environments, worktrees, .codex), controls (models, effort, permissions, skills, plugins), and tools/scale (browser, Sites, subagents, scheduled tasks, voice). It highlights AGENTS.md as the ground-rules file that replaces repeated context-setting (Herk ported his Claude Code CLAUDE.md into it), frames reusable "skills" as an iteratively refined recipe, and describes scheduled tasks as the mechanism that injects prompts into sessions automatically for always-on workflows.
x.comthreadPublished and added 4 Oct 2026🧠 AI Sujeet (@sujeetgholap) on X
A tweet arguing that Meta is using the credibility it earned from releasing open-weights Llama models to legitimize Muse, a free-as-in-beer service that bundles compute, weights, and apps rather than offering genuine open access. The commentary frames this as a strategic pivot from open-weights advocacy to a closed, Meta-controlled ecosystem play, explaining why Muse feels less aligned with the open-source AI movement than Llama was.
x.comthreadPublished and added 3 Oct 2026🧠 AI Dizzzank (@dank0296) on X
A Twitter thread recapping a "forward-deployed engineer" (FDE) talk on AI transformation methodology: find the real process a company runs (not the one it documents) by interviewing veteran staff and embedding engineers in the system of record, then sort every step into four buckets — delete, deterministic code, agentic (judgment plus exception history), or human-in-the-loop (payment, signing, negotiation). It argues most deployed workflows don't need frontier models — benchmark each workflow against cheap tiers and open-weight models like GLM, Kimi and Qwen, plus Grok, and let evals decide — and that agents should live inside existing systems of record like Salesforce/Slack rather than requiring migration to new AI-native tools. Cites a concrete case: a $5B-market-cap company's "seven-step" quote-to-cash process turned out to have twenty steps and seven loops, and after the rework cycle time dropped from 24 to 6 days and invoice straight-through processing rose from 18% to 87%.
x.comthreadAdded 2 Oct 2026, published 1 Oct 2026🧠 AI- Dan Kornas (@DanKornas) on X
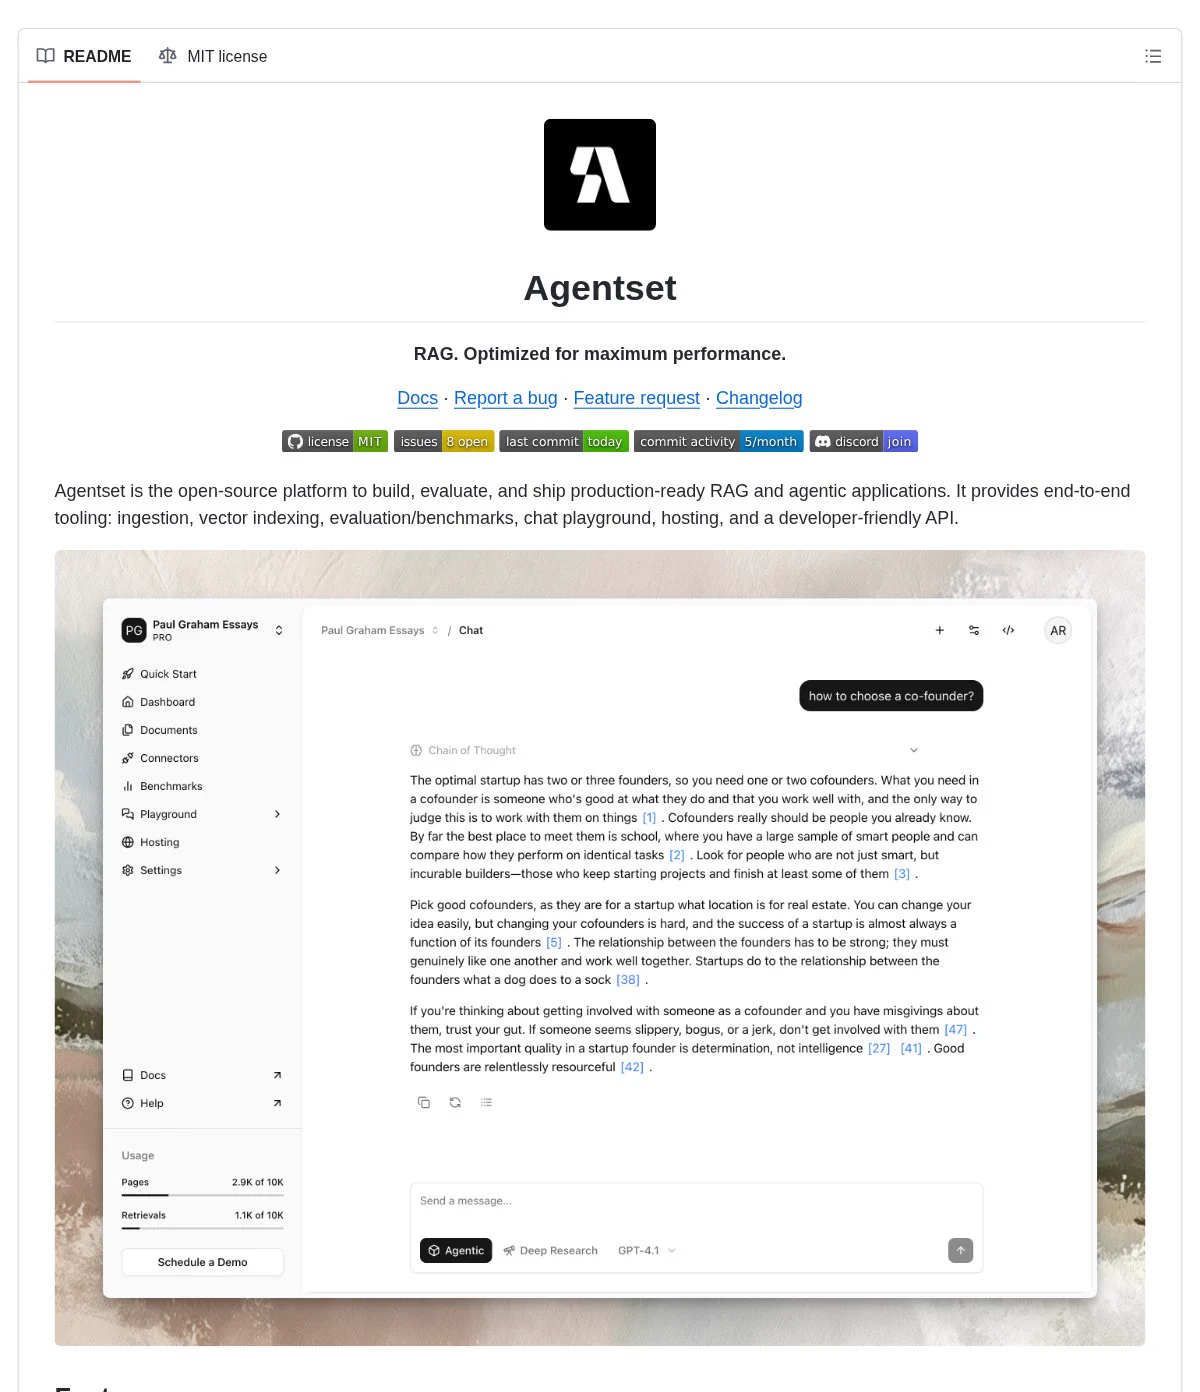
Agentset is an open-source (MIT-licensed) platform for building RAG and agentic applications, bundling ingestion, chunking, embeddings, retrieval, vector indexing, a citation-aware chat playground, evaluation/benchmark tooling, and a deployment layer (hosting, preview links, custom domains, typed SDKs, OpenAPI spec) into one codebase. It lets builders choose their own LLM, embedding model, and vector database rather than locking into a single stack.
x.comthreadPublished and added 1 Oct 2026🧠 AI - Samuel Zeng (@SamuelZengML) on X
Samuel Zeng announces the open-sourcing of Edge0's cross-platform app layer (iOS, macOS, Android, Windows), building on Edge0's earlier on-device 35B language model that runs in only 1-2.5GB of peak memory. The release includes app code, local model/runtime integration, model management, and build/deployment guides on GitHub; the technique keeps the full model on local storage and streams in only the experts (MoE-style) needed per step, predicting and prefetching the next experts while running storage reads in parallel with compute. A Q4 2026 roadmap promises a unified inference API across platforms plus Python, hardware-adaptive runtime, and a CUDA backend.
x.comthreadPublished and added 1 Oct 2026🧠 AI  USA SuperIntelligence | USASI (@USASIHQ) on X
Sevren released Heimr 570M, an experimental hybrid Mixture-of-Experts model designed for on-device use on phones and laptops, with about 570M active parameters out of 2.7B total. It is trained for a 64K context window to support long-context local decoding, targeting edge-AI deployment rather than cloud serving.
x.comthreadPublished and added 1 Oct 2026🧠 AI- LinuxSecurity (@lnxsec) on X
A security researcher breaks down a campaign where open-source offensive tools originally built for pentesting — Strix and Cairn — were combined with an orchestration layer called Hermes to form an automated discover-exploit-escalate-persist attack pipeline against AI agent deployments. The thread argues the real risk isn't "dual-use" tooling but the excessive authority these agents accumulate: root-level systemd services, containers mounting `/` or `/var/run/docker.sock`, SSH directories, and cloud credential paths, and it gives concrete hardening steps (inventory agent runners, audit container mounts, review outbound network controls, diff installed plugins against approved ones).
x.comthreadAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security  Sara Adams (@psycyber13nv) on X
An X thread breaking down what zero-knowledge proofs actually guarantee versus a simple hash-and-publish approach, covering the three required properties (completeness, soundness, zero-knowledge), the Fiat-Shamir transform for non-interactive proofs, and a practical comparison of zk-SNARK vs zk-STARK tradeoffs (proof size, trusted setup, post-quantum outlook). It ties the theory to real-world privacy use cases — W3C Verifiable Credentials, Microsoft's Vega mobile driver's license work, BBS/SD-JWT selective disclosure, and Bulletproofs range proofs — and flags limits like circuit bugs and leftover trusted-setup "toxic waste" that can produce valid-looking but false proofs.
x.comthreadAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security- Formal Verification of Execution and Consensus Clients
A reply on the Ethereum Research forum (ethresear.ch) responding to @pcaversaccio's call for formally verifying hard-fork changes in Ethereum execution and consensus clients before mainnet activation. It surveys current formal-verification efforts (Etheorem/SizzLean in Lean 4 for consensus/SSZ, Verifereum in HOL4 for the EVM), argues for prioritizing high-leverage surfaces like SSZ, state transition, fork-choice and core EVM semantics, and pushes for stronger verification tooling in Rust (Aeneas/Verus/hax) as an incremental path to reducing the trusted computing base of client software.
ethresear.chthreadAdded 29 Sep 2026, published 25 Sep 2026🛡️ Security - Retrochainer Post
A tiered hardware guide ("the ladder") for running local LLMs in 2026, ranking ten setups from a free existing laptop through Raspberry Pi 5, Jetson Orin Nano Super, Mac mini/Mac Studio, used RTX 3090, RX 7900 XTX, AMD Strix Halo (Ryzen AI Max+ 395), RTX 5090, up to the NVIDIA DGX Spark. It frames unified memory (not raw TOPS) as the real constraint on model size, gives concrete specs/prices/token throughput per rung, and walks through setting up Ollama + Open WebUI plus an OpenAI-API-compatible local endpoint, with cost comparisons against ChatGPT Plus/Claude Pro/Cursor subscriptions and n8n-based automation examples.
x.comthreadAdded 22 Sep 2026, published 1 Aug 2026🧠 AI














Showing 60 of 61
Show more