Appraisal by AI: Model-driven victim prioritization in the VOLTA infostealer
VOLTA (VOLTA-AUTODOXER) is a self-deleting Windows infostealer that, after theft and live session-based enrichment, POSTs an evidence bundle to OpenRouter so an LLM can rank the victim's assets by monetization value. It falls back across a Claude, Kimi and Gemini chain when a model refuses. Talos covers the builder model, the Chrome App-Bound Encryption bypass, the volta_debug.txt artifact and countermeasures such as blocking Chrome --headless.
 blog.talosintelligence.comwriteupPublished and added 31 Oct 2026🛡️ Security
 NIK C2: The new AI-enabled command-and-control framework
NIK C2 is a newly observed C2 framework with a Go-based 64-bit Windows implant that embeds an OpenAI Chat Completions client (ai_generate command), falling back to the victim's OPENAI_API_KEY. Talos details its 52+ commands, AES-256-GCM over WebSocket with HTTP fallback, credential, wallet and keystroke theft, screen-lock ransomware, AMSI bypass and anti-debug. It also lists a live C2 at 87.120.196[.]120 and total-sitevv[.]lol.
blog.talosintelligence.comwriteupPublished and added 29 Oct 2026🛡️ Security Putting models to the secure coding test: Security rules
Datadog Security Labs tests whether Project CodeGuard v1.4.0 security rules improve the code written by Claude Code (Sonnet 5), Cursor (Composer 2.5) and Codex (GPT 5.5). Each model built the same document portal app once. Only GPT 5.5 closed the cross-user document IDOR and improved clearly. Sonnet 5 and Composer 2.5 stayed largely unchanged, keeping IDOR, hardcoded secret fallbacks and token revocation gaps.
 securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 19 Oct 2026🧠 AI
- Putting models to the secure coding test: Security rules
Second post in a Datadog Security Labs series testing whether Project CodeGuard (v1.4.0) security rules improve code written by coding agents. Sonnet 5 (Claude Code), Composer 2.5 (Cursor) and GPT 5.5 (Codex) each built the same document portal, and the output was audited with Datadog Code Security and a Sonnet 5 code review. Only GPT 5.5 closed the cross-user IDOR; Sonnet 5 and Composer 2.5 stayed largely unchanged, including hardcoded JWT secret fallbacks and incomplete revocation.
securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 19 Oct 2026🛡️ Security  Package managers have an integrity problem
Trail of Bits tested 25 popular package managers with a Docker and mitmproxy harness that simulates a compromised package repository injecting malware into legitimate packages. Fewer than half enforce lockfile hashes by default, only two verified every download, and only Go verifies signatures by default. The post covers lockfile hash pitfalls (Pub, pnpm, Conan, CocoaPods, Composer), repository, developer and Sigstore signing, and Go's checksum database. It also proposes lockfiles that commit to a signing identity plus a transparency log.
 blog.trailofbits.comwriteupPublished and added 14 Oct 2026🛡️ Security
- Field Notes: EtherRAT Distributed Through a Legitimate Intune Workflow
DFIR case where a malicious MSI impersonating Advanced IP Scanner, sourced from a fake GitHub repo found via Bing, was imported by a customer into Microsoft Intune and deployed to four endpoints, running a Node.js-based EtherRAT chain. It traces the infections by correlating the MSI ProductCode, MDMAppInstaller/omadmclient process ancestry and Intune app inventory (Graph PowerShell query). It also covers renamed node.exe hash-hunting pitfalls, Ethereum RPC dead-drop C2 traffic, a screen-capture script and a second impersonating repo.
 dfir.chwriteupAdded 14 Oct 2026, published 13 Oct 2026🛡️ Security
 Revenge of the SD-WAN: Cisco Catalyst SD-WAN Manager Auth Bypass (CVE-2026-76504)
VulnCheck's exploit development team analyzes CVE-2026-76504, a critical zero-day authentication bypass in Cisco Catalyst SD-WAN Manager (vManage), reproduced to the point of a weaponized exploit. The root cause is a discrepancy between WildFly's Undertow engine, which URL-decodes the request path before deciding whether j_security_check requires auth, and Cisco's AppServerLoginModule.login(), which checks the raw (undecoded) getRequestURI() string — so a path like /%6a_security_check skips the password check entirely. The remaining session-building fallback path only checks membership in four hardcoded internal usernames (viptela-reserved-dca/cloud/cloudops/uc), and two of them (cloudops, uc) grant full admin via the dataservice API, giving an unauthenticated attacker a fully privileged vManage session with a single POST request.
 vulncheck.comwriteupAdded 8 Oct 2026🛡️ Security
 tensorlake NPM package compromised with Shai Hulud worm
Aikido details a new Shai-Hulud worm wave that compromised the tensorlake npm package (v0.5.144, 100k+ lifetime installs) via a hijacked GitHub maintainer identity. The malware's preinstall script drops the Bun runtime to run an obfuscated payload that exfiltrates CI/cloud secrets, browser crypto-wallet extension data (via a bundled HackBrowserData binary), uses a blockchain dead-drop (an Ethereum contract queried via public RPC nodes) to resolve a fallback C2, and includes a GitHub-token-triggered dead-man's switch that wipes infected machines. The post includes full IOCs: file hashes, the C2 domain iseekaigogo[.]com, and the threat actor's wallet/contract addresses.
 aikido.devwriteupPublished and added 8 Oct 2026🛡️ Security
 Six defects in one signature verification tool, found from outside in six rounds
A forum writeup on ethresear.ch describing a "predictions-first" testing methodology for verification logic, applied against the author's own repository and against a live third-party MCP server (nsgoods Workbench, which offers offline signature verification over the x402 payment catalogue). Six rounds of testing surfaced concrete defects: a false negative caused by a stripped field list, a tamper-accepted body via a service-selection parameter that let callers choose which fields were excluded from the signed message, schema-rejection and signature-failure returning byte-identical error text, and a logging/privacy gap in the operator's system that was fixed after disclosure. The author ships a companion tool, exactzk-verification-guards, which captures both a passing and an actually-reproduced failing run as regression evidence rather than a fabricated example.
 ethresear.chwriteupPublished and added 2 Oct 2026🛡️ Security
- The First 24 Hours: What Happens When Ransomware Lands
An hour-by-hour ransomware incident response playbook written by UnderDefense CEO Nazar Tymoshyk and published on Huntress's blog, covering confirmation, containment, exfiltration detection, backup/recovery pitfalls, and root-cause investigation in the first 24 hours of an attack. It draws on Mandiant's M-Trends 2026 report (14-day median dwell time, 22-second access-broker-to-ransomware handoff) and CISA's November 2025 Akira advisory (VPN without MFA as primary access vector, exfiltration via FileZilla, WinRAR, WinSCP, RClone, Mega and Ngrok, credential dumping with Mimikatz and LaZagne, PowerShell-based shadow copy deletion) alongside real UnderDefense engagement anecdotes.
 huntress.comwriteupAdded 3 Oct 2026, published 2 Oct 2026🛡️ Security
 The MCP Ecosystem Is Speaking Five Revisions at Once
A dated research report (Pennyforge, 2026-10-02) that probes the live MCP ecosystem to show it is fragmented across five spec revisions at once: it POSTs initialize/server/discover calls against 186 deduplicated endpoints pulled from the official MCP registry's v0 API, plus 10 popular npm stdio servers spawned via npx. It finds only ~9.7% of responding endpoints speak the new stateless 2026-07-28 wire (which removes Mcp-Session-Id, the initialize handshake, and adds server/discover), that the flagship @modelcontextprotocol/server npm packages still only speak the older 2025-06-18 revision, and documents a "version-echo" methodology pitfall where servers negotiate within a supported range rather than reporting a fixed version — illustrated with a parallel failure mode found in the x402 payment protocol.
 dev.towriteupPublished and added 2 Oct 2026🧠 AI
 How we found 24 Android vulnerabilities using our open source AI security agent
GitHub Security Lab describes custom "taskflow" prompts built on their open-source Taskflow Agent to hunt Android app vulnerabilities, reporting 24 findings to date. It walks through two concrete chains: an exported, unprotected MapActivity in OsmAnd that lets any app silently import settings and exfiltrate the user's exact map tile/route coordinates to an attacker server, and a hostname-parsing logic bug plus overly loose cookie-domain check in the Wikipedia Android app that lets a wikipedia:// deeplink load an attacker page (e.g. evil-wikipedia.org) and steal long-lived session cookies for account takeover. The post also candidly notes where LLMs struggle (false positives, mis-estimating severity, missing mitigating factors) versus where they excel (deep knowledge of safe/unsafe API patterns).
 github.blogwriteupAdded 7 Oct 2026, published 28 Sep 2026🛡️ Security
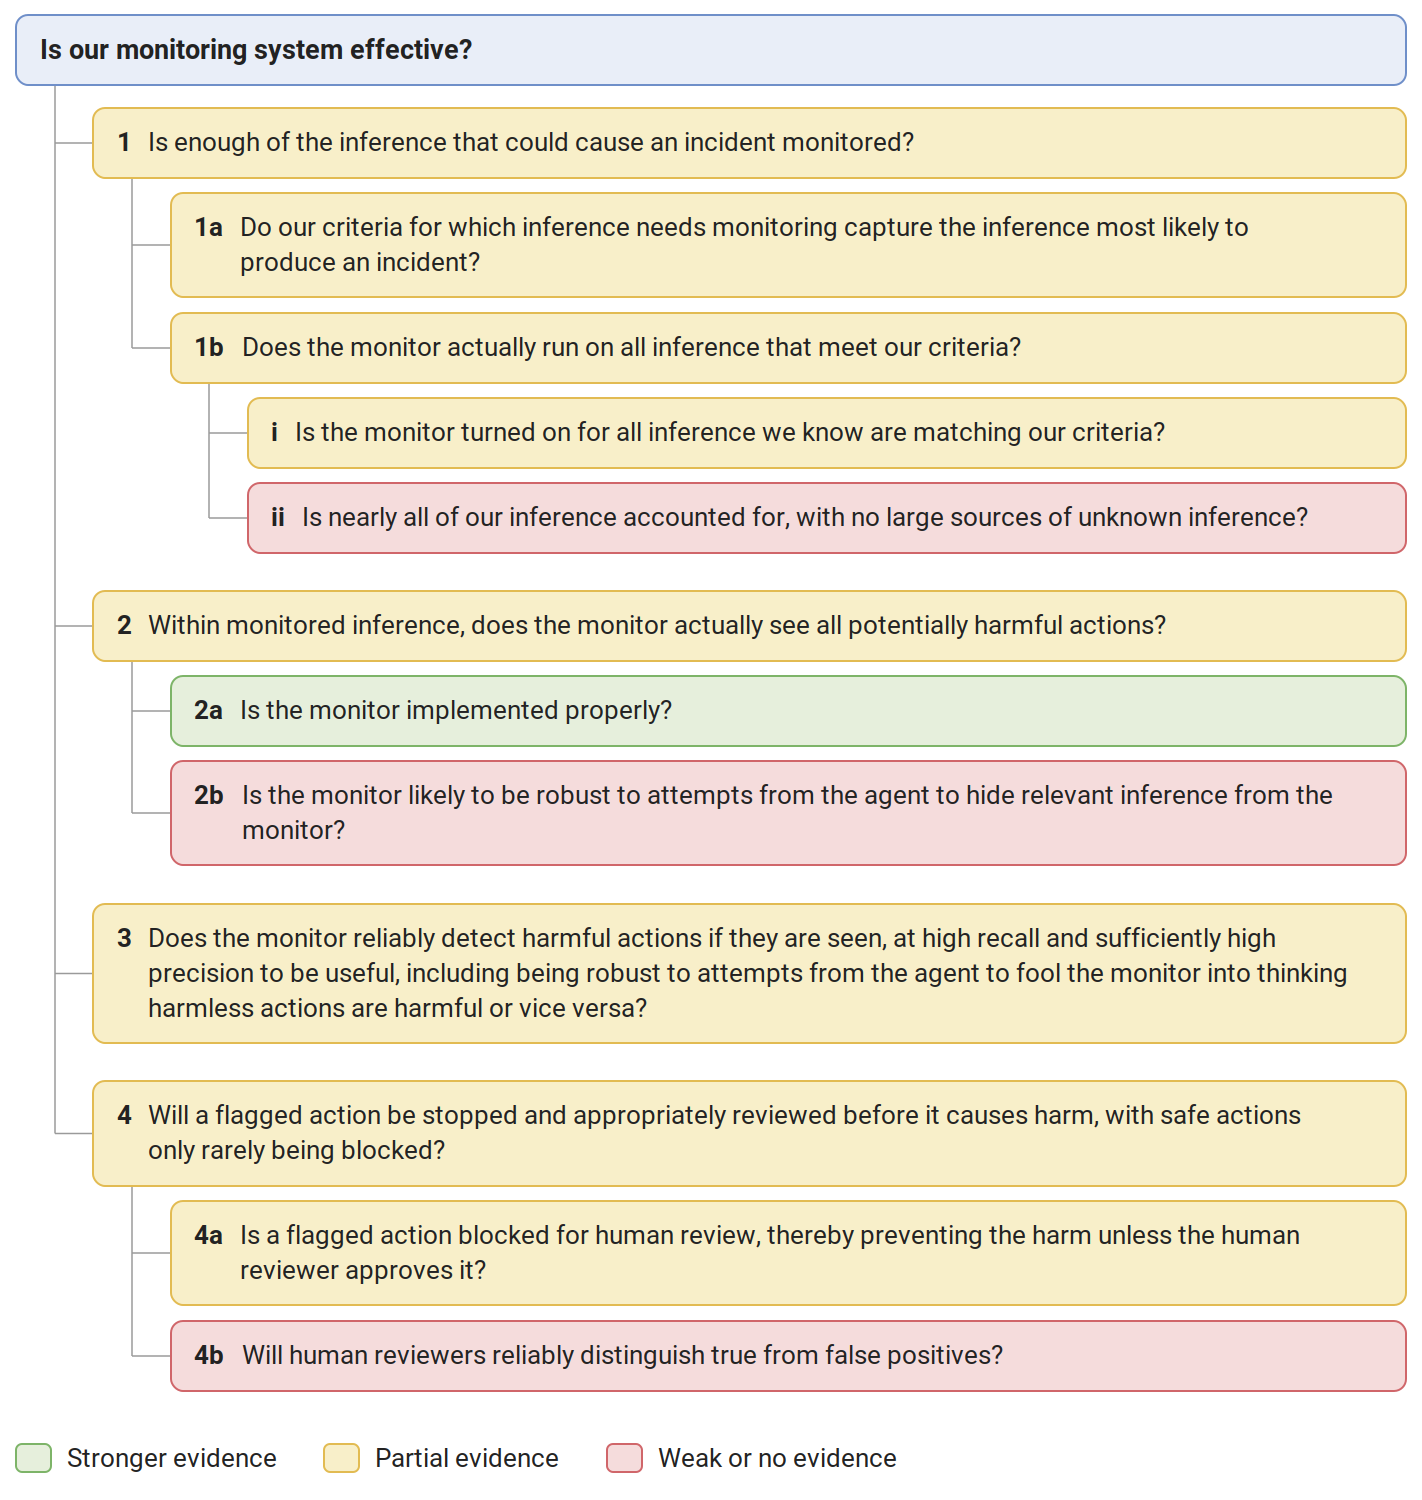 Implementing and Evaluating a Basic Per-Action Monitor for Safer Evals
METR describes a per-action monitor built as an Inspect approver. An LLM judge scores each agent tool call before execution, and calls scoring 3/10 or higher halt the eval for human review. It lays out four claims needed to argue the monitor works, with evidence and gaps. Reported results: 0.025% false positives on 20,000 actions, and a spoofed user turn lowered suspicion scores.
 metr.orgwriteupAdded 29 Oct 2026, published 27 Sep 2026🧠 AI
- Implementing and Evaluating a Basic Per-Action Monitor for Safer Evals
METR describes a live per-action LLM monitor, built on Inspect's approver chain, that blocks agent tool calls scoring 3/10 or higher for human review during evals. It lays out four conjunctive claims for effectiveness with evidence gaps. Results include 0.025% false positives on 20,000 actions, 10/10 UK AISI incident transcripts caught, and a spoofed user turn that lowered scores, with 12/30 runs falling below the threshold.
metr.orgwriteupAdded 29 Oct 2026, published 27 Sep 2026🛡️ Security  Top 10 attacks on Claude Code and what each one actually broke
Adversa AI catalogs ten distinct Claude Code attacks documented between September 2025 and September 2026: the Miasma supply-chain worm that hit 73 Microsoft repos via a SessionStart hook, TrustFall's unsandboxed MCP server execution on folder-trust, Check Point's CVE-2025-59536/CVE-2026-21852 pre-trust-dialog code execution and API key theft, Sentry-DSN-based "Agentjacking" prompt injection via fake bug reports, a 50-subcommand cap that silently disables deny rules, the SymJack symlink-to-config-hijack primitive working across six agent CLIs, Wiz's GhostApproval deceptive-approval-prompt finding (with CVE-2026-12958 at AWS and CVE-2026-50549 at Cursor but none at Anthropic), the Plugin4Shell SHA/branch-name collision bypassing plugin pinning, an academic MCP tool-poisoning paper achieving RCE on agent/LLM pairs, and SkillCloak's self-extracting-packer bypass of skill scanners. The piece argues almost none of these are model-behavior bugs - they are trust-boundary and consent failures in the surrounding tooling - and closes by pitching Adversa's own runtime agent security gateway as the fix.
 adversa.aiwriteupAdded 7 Oct 2026, published 23 Sep 2026🛡️ Security
 Auditing in the age of (good enough) AI
Trail of Bits describes preparing for a six-month audit of the Miden zkVM (a zero-knowledge VM with its own custom assembly language, MASM) by having AI agents (Claude and Codex) build an LSP server, a decompiler, an abstract-interpretation-based static analysis engine, and a Lean formal model of the VM executor, none of which previously existed for MASM. These tools surfaced a high-severity bug in the mod_12289 procedure where an underconstrained prover-supplied advice value allowed a malicious prover to forge Falcon signatures and drain Miden accounts, plus over 400 type-validation issues, while the Lean proof effort produced 95 machine-checked correctness proofs and caught two additional subtle arithmetic bugs (rotr, wrapping_mul) missed by unit tests.
blog.trailofbits.comwriteupPublished and added 18 Sep 2026🛡️ Security HEAVYGRAM: A Telegram-based Surveillance Backdoor Linked to Handala Hack
Group-IB documents previously undocumented samples of HEAVYGRAM, a Python/PyInstaller-based Windows backdoor that uses the Telegram bot API for command-and-control, screen/audio capture, data exfiltration, and DLL side-loading, alongside the related CRUDEEXCLUDE loader that adds Windows Defender exclusions. The research corroborates and extends a March 2026 US DOJ affidavit and FBI FLASH report, attributing the malware with moderate confidence to the Handala Hack persona — assessed as a false-flag "hacktivist" front for Void Manticore (aka Storm-0842/Banished Kitten), operating on behalf of Iran's MOIS — used since Fall 2023 against Iranian dissidents, journalists, and critics of the Iranian government via Telegram-delivered, Delphi-packaged lures (fake KeePass, Telegram, Pictory apps). It details four infection-chain variants (WSF/VBS downloaders, HTA Telegram-polling scripts, Delphi droppers with embedded archives), the implant's command prefixes (@@/**/##) and attachment handlers, dual-bot C2 configurations, and provides IOCs and detection/hardening recommendations.
 group-ib.comwriteupAdded 1 Oct 2026, published 17 Sep 2026🛡️ Security
 Passkey-themed social engineering leads to identity and cloud compromise
Microsoft Security Research details an active campaign (since May 2026) where attackers use voice-phishing and SMS lures impersonating IT helpdesk passkey/SSO enrollment requests to drive victims into AiTM or device-code phishing flows, compromising Microsoft 365 identities. Post-compromise, actors register attacker-controlled MFA methods (e.g., software OTP tokens) for persistence, conduct systematic Microsoft Graph reconnaissance across users, groups, roles, and SharePoint/OneDrive/Exchange, then exfiltrate data at a measured pace using automated Node.js/python-httpx tooling while evading detection through IP rotation and anonymous proxies. The post includes real audit-log JSON examples, multiple KQL hunting queries for GraphAPIAuditEvents/CloudAppEvents, full MITRE ATT&CK mapping, and attributes the initial-access tradecraft to Storm-3121 and Storm-3032, which feed into ShinyHunters/Falcon and Helix extortion operations.
 microsoft.comwriteupAdded 3 Oct 2026, published 9 Sep 2026🛡️ Security
 Dark Caracal Reloaded: GoCaracal — New Go Malware With Ethereum-Based C2 Fallback
Arctic Wolf Labs documents GoCaracal, a previously undocumented modular Go-based malware framework attributed with medium confidence to Dark Caracal (linked to Lebanon's GDGS), deployed alongside an updated Bandook variant in a June 2026 intrusion against a Venezuelan communications organization. The extended GoCaracal build features a novel Ethereum smart-contract (BulletproofC2) fallback that lets operators update C2 addresses via on-chain transactions without redeploying malware, and analysis of 249 samples traces the framework's four-phase development from January to July 2026. The report includes delivery-chain details (SVG phishing, URL shorteners, Delphi loader), infrastructure analysis (AEZA Group, AlexHost hosting), a YARA rule, and IOCs for detection.
 arcticwolf.comwriteupAdded 26 Sep 2026, published 26 Aug 2026🛡️ Security
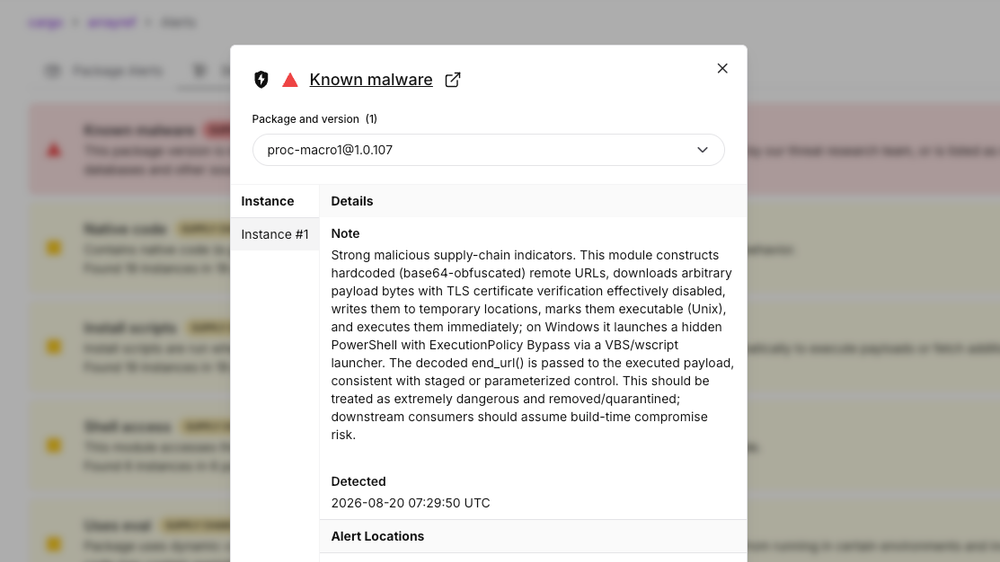 Socket: Popular Rust Crates Compromised in Build-Time Supply Chain Attack
Socket's Threat Research Team documents a supply chain attack in which three legitimate Rust crates (arrayref, internment, append-only-vec) maintained by droundy were republished with a dependency on proc-macro1, a typosquat of proc-macro2 whose build.rs downloads and executes cross-platform malware during Cargo compilation. The stage-2 backdoor profiles the host, inventories Chromium browser login origins and extensions, establishes user-level persistence (HKCU Run key, systemd service, or LaunchAgent), and beacons to a C2 with a DGA fallback of ten date-based domains, with all analyzed variants sharing the same embedded RSA key. The report includes full IOCs (C2 IPs, payload hashes, host artifacts, DGA domains) and remediation guidance for CI/CD and developer environments that built the malicious versions.
 socket.devwriteupPublished and added 20 Aug 2026🛡️ Security
 Rust Supply Chain Attack on arrayref: Significant Overlap with DPRK Campaigns
Wiz researchers found that malicious versions of the Rust crates arrayref, internment, and append-only-vec were published to crates.io, each pulling in a typosquatted build-dependency (proc-macro1, mimicking proc-macro2) whose build.rs executes a remote payload at compile time. The payload beacons to a C2 endpoint (/49890878) shared with the Mastra campaign, disables TLS validation, enumerates Chrome/Brave/Edge saved logins via their SQLite stores, persists via Registry Run keys/LaunchAgents/systemd, and falls back to a DGA — with C2 infrastructure and SSL-issuer overlap tying it to DPRK/Sapphire Sleet activity previously seen in the Mastra and axios supply chain attacks. arrayref is used in roughly 75% of Rust environments, making this a high-impact build-time compromise.
 wiz.iowriteupAdded 3 Sep 2026, published 20 Aug 2026🛡️ Security
 Putting models to the secure coding test: Plan vs default mode
Datadog Security Labs ran one document-portal prompt through Sonnet 5, Composer 2.5 and GPT 5.5 in default and plan mode, giving six apps. Code review found an IDOR flaw in every one, and Composer 2.5 plan mode shipped a hardcoded JWT secret fallback. The author found no meaningful link between plan mode and more secure code, and says the prompt mattered more than the mode.
securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 19 Aug 2026🧠 AI- MacSync Stealer: How a Google Search for Claude Led to a macOS Infostealer
Huntress SOC analysts reverse-engineer MacSync, a macOS infostealer/RAT distributed via a sponsored Google Ads link to a fake "Apple Support"-branded claude.ai shared conversation that uses ClickFix to trick victims into pasting a curl/zsh loader into Terminal. The six-stage chain runs a polymorphic gzip/Base64 loader, an in-memory AppleScript stealer that harvests Chromium Safe Storage keys, keychain secrets, Telegram/SSH/cloud credentials, abuses TCC (Full Disk Access and Screen Recording) prompts, drops a Mach-O RAT with WebSocket/TLS C2 and an XOR-obfuscated fallback domain, and trojanizes 84 crypto wallet extensions/apps to phish seed phrases. The piece also compares it to prior AMOS Stealer and SectopRAT ClickFix campaigns and offers behavior-based detection guidance.
huntress.comwriteupAdded 3 Sep 2026, published 17 Aug 2026🛡️ Security  Socket: 737 Malicious VPN/Proxy Chrome Extensions Impersonate 66 Brands
Socket's Threat Research Team documents a 737-extension Chrome Web Store campaign ('Myxa VPN' / Муха VPN) that impersonates 66 legitimate VPN/privacy brands (Proton VPN, NordVPN, AmneziaVPN, AntiZapret, Cloudflare 1.1.1.1, etc.) to lure Russian-speaking users seeking censorship circumvention. The extensions force all browser traffic through a shared SOCKS5 proxy pool via chrome.proxy.settings, evade DNS-based blocklists using DNS-over-HTTPS to resolve proxy hosts, sell non-existent premium server locations, ship fake license checks, add remote-configuration code post-approval, and submit false 'no data collection' justifications to Chrome reviewers. The report ties the operation to a single Russian self-employed-registered VPN business via shared Yandex Metrika counters, build-path leakage, bulk domain registration, and a Telegram-based billing dashboard, and notes 516 of the 737 extensions remain live despite prior Palo Alto Networks disclosure.
socket.devwriteupPublished and added 12 Aug 2026🛡️ Security Russian AI Slopsquatting Publishes 700+ Malicious NPM Packages
OpenSourceMalware documents WEL1DROPPER (aka Flooding Dropper), a campaign that published 788+ slopsquatted npm packages (e.g. checkout-mobile-bnpl) which execute on require() with no install script, downloading cross-platform RAT/infostealer payloads via rotating Cloudflare Workers URLs with a DNS TXT-record fallback channel. The writeup reverse-engineers the Linux (UPX-packed ELF) and macOS (universal Mach-O) second-stage payloads, detailing anti-analysis checks, LaunchAgent persistence disguised as com.apple.windowserver.helper, XOR-obfuscated C2 domains, a suspected Sliver C2 final stage, and ties the campaign to Russian financial-sector lures and the earlier Moika npm campaign.
 opensourcemalware.comwriteupAdded 3 Sep 2026, published 6 Aug 2026🛡️ Security
 Compromised npm Packages: @joyfill/components and @joyfill/layouts Ship an Obfuscated Remote Access Trojan
StepSecurity dissects malicious beta versions of @joyfill/components and @joyfill/layouts published to npm on July 28, 2026, which inject a five-stage obfuscated payload that executes on import rather than via a postinstall hook, so npm install --ignore-scripts does not stop it. The chain resolves its C2 server by reading a transaction on the Tron blockchain (with Aptos as fallback), decrypts a BNB Smart Chain transaction to find the next stage, and deploys a Socket.IO remote access trojan with worm-like self-propagation that patches the global npm CLI, VS Code/Cursor's @vscode/deviceid module, Discord desktop, and GitHub Desktop, plus a Python credential stealer targeting browser data, wallets, and Git/GitHub tokens. The writeup includes fully deobfuscated source code, IOCs (C2 IPs, Tron addresses, file hashes), and results from detonating the packages under Harden-Runner in a sandbox.
 stepsecurity.iowriteupAdded 3 Sep 2026, published 30 Jul 2026🛡️ Security
- How I Found Open-Source 0-days with an LLM Multi-Agent Workflow
A student researcher describes an LLM multi-agent pipeline (GLM-4.7 for candidate finding, GLM-5 for semi-triage, Codex 5.3 for final triage) built to hunt logic and authorization bugs in large open-source codebases like Grafana, Nextcloud, Matomo, Airflow and protobuf. The post details the prompt-engineering fixes (forcing the model to explicitly reason about attacker conditions, server conditions, and CIA-triad impact) that cut false positives, and lists the resulting real vulnerabilities, including CVE-2026-21721, a CVSS 8.1 privilege escalation in Grafana's dashboard permissions API caused by a missing UID scope check in ac.EvalPermission.
 blog.cykor.krwriteupPublished and added 29 Jul 2026🛡️ Security
 How we use /goal to find bugs in Patch the Planet
Trail of Bits describes how they use Codex's /goal feature, an open-ended agentic objective mode, to hunt for bugs in heavily audited open-source codebases like Rust, curl, and zlib as part of the OpenAI-backed Patch the Planet initiative. Key techniques include letting Codex write and red-team its own goal prompts, defining precise outcomes rather than prescribing methods, running one outcome per agent to avoid competing objectives, and building an automated variant-analysis pipeline (using P-critical Rust issues, a security gate, and a two-pass false-positive judge) that produced a soundness hole and a miscompilation patched in Rust 1.98, plus privilege-escalation bugs in Keycloak's SAML component. They also built agentcov, an internal tool that tracks code coverage read by Codex to prevent it from skipping parts of the codebase.
blog.trailofbits.comwriteupAdded 3 Sep 2026, published 28 Jul 2026🛡️ Security- From Container Escape to Cloud Takeover
Lab-based cloud security assessment covering four attack paths: a privileged hostPID pod escaped to the node with nsenter, deleting the kube-apiserver static pod manifest to crash the control plane, Trivy Operator vulnerability reports piped into BigQuery, and a malicious PR exploiting a pull_request_target workflow that checks out PR code to steal a GCP Workload Identity Federation token via Terraform's external data source during plan. Each section pairs the exploit with defenses (Pod Security Standards, Kyverno/Gatekeeper, Falco rules, split plan/comment workflows, least-privilege service accounts) and ties them into one kill chain.
 medium.comwriteupAdded 3 Sep 2026, published 26 Jul 2026🛡️ Security
 Better generic secrets detection starts with finding non-secrets
Aikido Security engineers describe how they built a 'publishable credentials denylist' for their Betterleaks secret scanner to suppress known-public keys (like Stripe's publishable API key) that generic secret-detection regexes otherwise flag as false positives. They tested the change against 100GB of Common Crawl data, cutting false positives by 2.37% (27,886 fewer findings), and outline five edge-case categories (unique shape, no unique shape needing context, same shape as secret needing liveness checks, sensitive-if-misconfigured keys, and test/sandbox credentials) that complicate cleanly filtering public-by-design credentials from real secrets.
aikido.devwriteupAdded 3 Sep 2026, published 23 Jul 2026🛡️ Security AI Security Briefing
Adversa AI's "GuardFall" research shows that decades-old shell tricks (quote removal, $IFS expansion, command substitution, base64-to-sh piping, and destructive argv flags like `find -delete`) let prompt-injected content bypass the pattern-matching shell-command guards in most popular open-source AI coding agents, because the guards inspect raw command strings while bash rewrites them before execution. Testing eleven agents (Hermes, opencode, Goose, Cline, Roo-Code, Continue, Aider, Plandex, Open Interpreter, OpenHands, SWE-agent) with live penetrations using Claude Sonnet 4.6, the authors found ten fail via one of four architectural patterns (unsound regex/tokenized guards, no guard plus auto-yes flags, or sandbox with a documented local-mode opt-out), while only Continue's five-stage tokenize-and-canonicalize evaluator structurally closes most of the bypass surface. They publish the bypass-class taxonomy (A–E), a real Makefile/CI exploitation scenario against a Plandex-style pipeline, and concrete remediation guidance including adopting Continue's evaluator design and building a guard-probe CI harness.
adversa.aiwriteupPublished and added 18 Jul 2026🛡️ Security Coordinated AsyncAPI Supply Chain Attack: Miasma RAT Delivered via Compromised CI/CD Pipelines in Two Repositories
On July 14, 2026, attackers compromised push access to two AsyncAPI GitHub repositories (asyncapi/generator and asyncapi/spec-json-schemas) and pushed malicious commits under a placeholder git identity that triggered legitimate CI/CD release workflows (release-with-changesets.yml, if-nodejs-release.yml), publishing five malicious npm package versions (@asyncapi/generator, generator-helpers, generator-components, specs) carrying a runtime-triggered obfuscated dropper for the Miasma RAT, complete with valid OIDC/SLSA provenance attestations. StepSecurity detected the packages within 30 minutes, used Harden-Runner in an isolated GitHub Actions job to capture the malware's C2 traffic (HTTP plus IPFS/Nostr/BitTorrent DHT fallback channels), and pushed the IOCs to their Global Block List to block exfiltration across customer pipelines; all malicious versions have since been unpublished.
stepsecurity.iowriteupAdded 3 Sep 2026, published 16 Jul 2026🛡️ Security Socket: 11 Malicious NuGet Tools Pose as Game Cheats
Socket's Threat Research Team analyzed 11 malicious NuGet DotnetTool packages (published by account pepegit666) that impersonate game cheats/bots for titles like GTA5RP, Albion Online, and Throne and Liberty. Each package's .NET downloader resolves GitHub hosts via DNS-over-HTTPS, requests UAC elevation to resync the clock, and fetches a PyInstaller Windows payload (pepesoft.exe) from GitHub Releases/Hugging Face with dormant BitTorrent fallback code, that in turn authenticates to Google Sheets for telemetry, hardware-binds licenses, enforces a remote HWID ban-list, and, in three samples, drives Telegram bot commands that exfiltrate screenshots and modify Windows Installer registry keys on exit. The report includes full IOC lists (hashes, domains, hardcoded AWS-style keys, mutex GUID) and MITRE ATT&CK technique mappings.
socket.devwriteupPublished and added 15 Jul 2026🛡️ Security- AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress
Huntress recovered and reconstructed "Untitled1.ps1," a PowerShell Active Directory enumeration script used by an attacker during a June 3 incident via RDP access with compromised credentials, and identified it as AI-generated ("vibe-coded") based on artifacts like an unedited LLM placeholder hostname, a "FULLY FIXED" prompt-iteration title, over-engineered five-method DC-discovery fallback logic, and gratuitous colored console/HTML reporting output. The attack chain paired this bespoke recon tool with off-the-shelf abuse of s5cmd (legitimate AWS S3 CLI used for exfiltration) and SharpShares (share enumeration), illustrating how LLM-generated one-off malware evades hash/signature-based detection and pushes defenders toward behavioral analytics on Active Directory enumeration patterns.
huntress.comwriteupAdded 3 Sep 2026, published 8 Jul 2026🛡️ Security  Socket: 152 Chrome Live Wallpaper Extensions Hid Ad Tracking and Faked Google Search Traffic
Socket's Threat Research Team uncovered a family of 152 Chrome 'live wallpaper' new-tab extensions, built from one shared codebase and spread across 38 publisher accounts and three brand backends (tabplugins.com, yowgames.com, chromewallpaper.com), with ~105,000 combined installs. A 54-listing subset forges Google organic-search attribution via fake utm_source=google tags and a cloaked google.com/url uninstall redirect carrying spoofed ved/usg tokens, while every listing falsely claims 'no data collected' on the Chrome Web Store despite its own linked privacy policy admitting IP/ISP/click logging shared with AdSense, DoubleClick, and ad partners. All 141 verified samples also ship an undisclosed, inert IndexedDB enumerate-and-delete anti-forensic routine on every service-worker start.
socket.devwriteupPublished and added 13 Jun 2026🛡️ Security Mobile Network Hacking: Recon on Local Mobile Networks
A Hackers-Arise tutorial demonstrating use of FALCON (Fast Analysis of LTE on Control Channels), an srsRAN/srsLTE-based tool, together with DragonOS and a LimeSDR/USRP B210 to decode the PDCCH of local 4G/5G cell towers. It explains how capturing DCI, RNTIs, and resource allocation data can be abused for passive traffic interception, subscriber tracking via RNTIs, and targeted denial-of-service by identifying cell capacity limits.
 hackers-arise.comwriteupAdded 3 Sep 2026, published 5 Jun 2026🛡️ Security
- Aikido vs XBOW: AI Pentest Platforms Compared
Doyensec compared Aikido's Attack AI Pentest against XBOW's Lightspeed, two AI-powered application security testing platforms, manually validating every reported finding as a true or false positive. The evaluation covers configuration workflow, impact on the tested application, report quality, cost, and speed, giving an independent view of current AI pentesting maturity.
 blog.doyensec.comwriteupAdded 3 Sep 2026, published 4 Jun 2026🛡️ Security
 VSCode Lifecycle Script Malware
Explains how npm's preinstall/install/postinstall lifecycle scripts and VS Code's tasks.json "runOn": "folderOpen" setting (paired with reveal:never/echo:false to suppress output) are exploited by threat actors as silent code-execution triggers requiring no user action beyond routine developer workflows like npm install or opening a project folder. Covers why this bypasses reachability-based defenses since malware "goes boom without a path," and walks through real npm attack campaign examples including one referencing Bitward.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 16 May 2026🛡️ Security TrustFall: 1-click coding agent RCE in Claude, Cursor, Copilot
Adversa AI's TrustFall report shows that Claude Code, Gemini CLI, Cursor CLI, and Copilot CLI all auto-execute project-defined MCP servers as unsandboxed OS processes the instant a user accepts the generic folder-trust prompt, with no mention of code execution in Claude Code's v2.1+ dialog. A malicious repo needs only two JSON files (.claude/settings.json with enableAllProjectMcpServers/enabledMcpjsonServers/permissions.allow, plus an inline-payload .mcp.json) to achieve one-Enter-keypress RCE with full user privileges, and the same chain runs with zero human interaction against CI runners using the official claude-code-action since headless mode skips the trust dialog entirely. The report documents Anthropic's declination of the finding as intended behavior, contrasts it with the stricter bypassPermissions warning flow, references the related CVE-2025-59536 patch, and ships defender mitigations (managed-settings lockdown, config auditing, CI branch restrictions) plus a safe PoC.
adversa.aiwriteupAdded 20 May 2026, published 7 May 2026🛡️ Security- Serious Cryptography (book review)
A detailed personal review of the first edition of 'Serious Cryptography: A Practical Introduction to Modern Encryption' by Jean-Philippe Aumasson (No Starch Press, 2017), aimed at non-cryptographer engineers. The reviewer highlights the book's chronological structure from basic concepts through symmetric and asymmetric crypto to post-quantum cryptography, praising its accessible AES walkthrough, MAC vs HMAC distinctions, elliptic curve explanations, and 'How things can go wrong' sections that tie real implementation pitfalls to actual vulnerabilities — useful reference material for vulnerability researchers and pentesters needing solid crypto fundamentals.
 bencteux.frwriteupAdded 3 Sep 2026, published 25 Apr 2026🛡️ Security
- The 60ms Window: How Event 5156 Solves the ADWS Attribution Problem
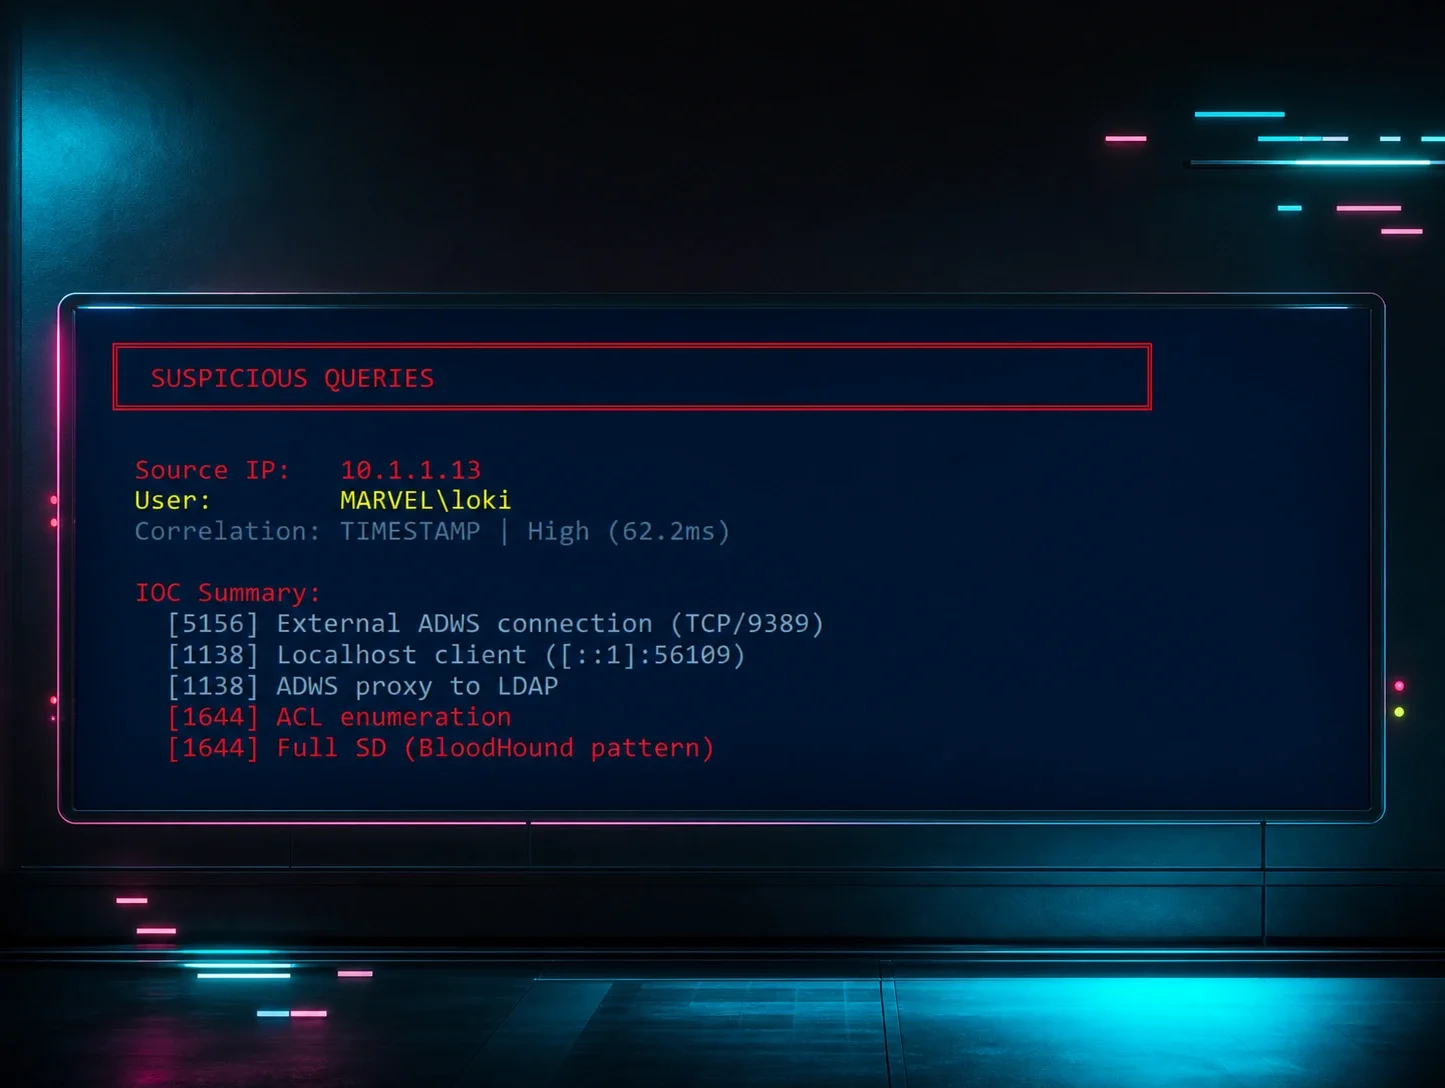
Huntress researchers solve the long-standing 'ADWS attribution problem' where tools like SOAPy abuse Active Directory Web Services to hide the attacker's real source IP behind localhost ([::1]) in LDAP diagnostic logging (Event 1644). By correlating Windows Filtering Platform Event 5156 (which captures the real inbound source IP on port 9389 before ADWS proxies to loopback) with Event 1138 (ADWS session) and Event 1644 (LDAP query) using a stable ~60-80ms timestamp window, they demonstrate reliable attribution even when port-based correlation fails due to log rollover. The post includes a released PowerShell script (Get-ADWSAttribution.ps1) and addresses the false-positive concern of RSAT tools also using ADWS via pattern detection on suspicious 1644 query attributes.
huntress.comwriteupAdded 3 Sep 2026, published 9 Apr 2026🛡️ Security 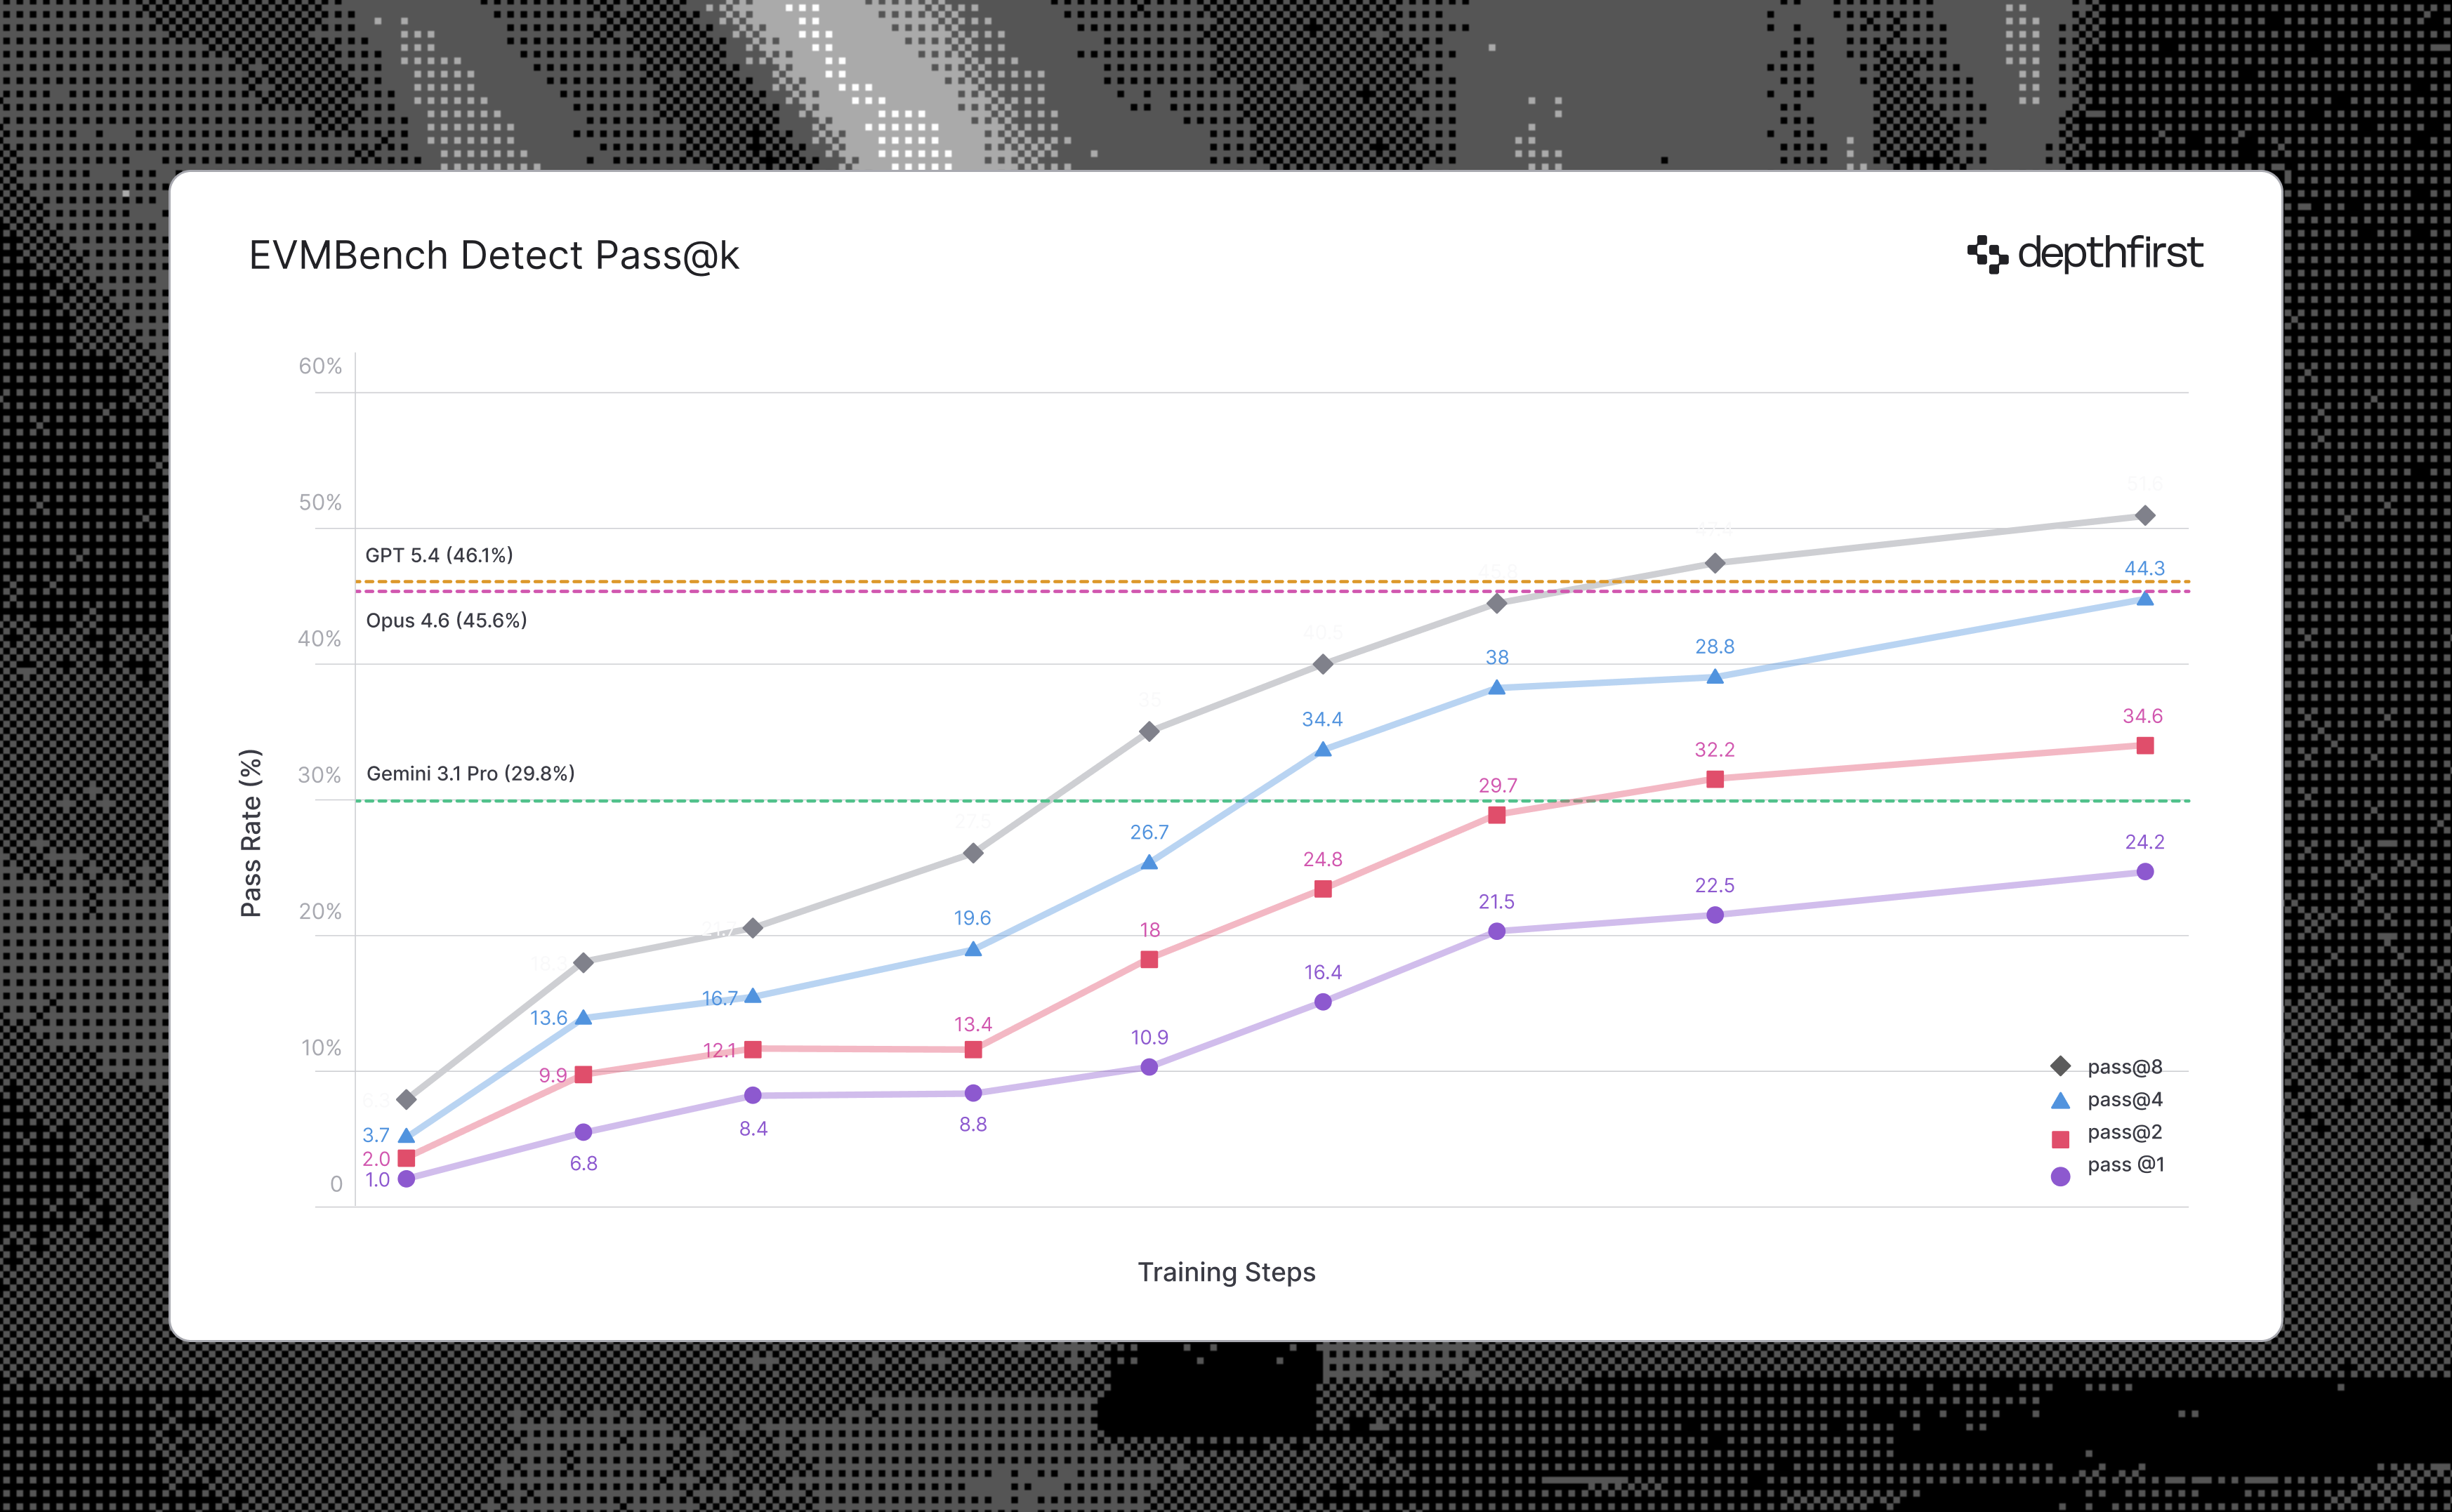 Training State of the Art Vulnerability Discovery Agents through Reinforcement Learning | depthfirst
dfs-mini1 is a vulnerability detection agent from depthfirst, built by reinforcement learning on gpt-oss-120b with a shell-only harness. Trained in Kubernetes sandboxes on audits that do not overlap EVMBench, using a 32k context with learned summarization, it reaches state of the art on EVMBench Detect at pass@8 at 10-30x lower cost than frontier models. It also transfers to an internal CVE benchmark, but reports more false positives.
 depthfirst.comwriteupAdded 30 Oct 2026, published 31 Mar 2026🧠 AI
- How Threat Actors Abuse Remote Management Tools | Huntress
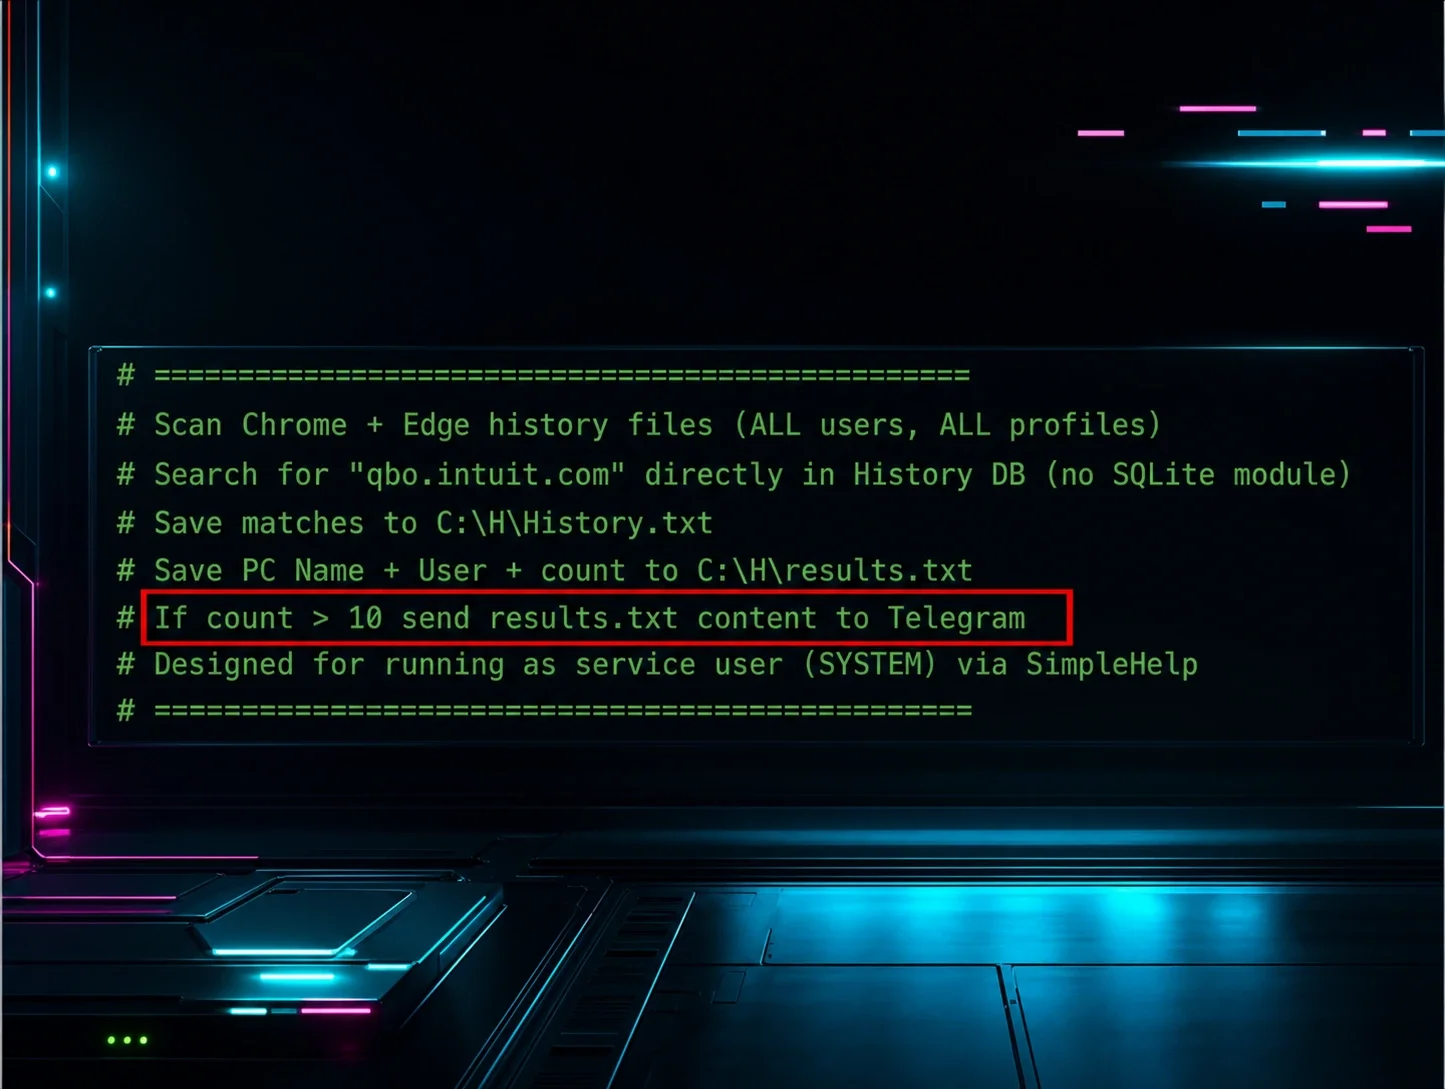
Huntress details how low-skill threat actors daisy-chain legitimate RMM tools (ScreenConnect, Action1, HeartbeatRM, AnyDesk, Atera, etc.) via invitation and Social Security themed lures, LLM-generated infostealer scripts, and multi-fallback browser download tricks hosted on GitHub repos (VH851, Drasticc) to gain and disguise persistent access. It also documents firsthand observation of an actor who signed up to Huntress itself, revealing their toolchain (DeepSeek, Email Extractor, Proxy SwitchyOmega, 9Proxy, CertifyTheWeb, Sordum Hide from Uninstall List, and a fake Windows Security PIN harvesting binary pin.exe) and victim data such as W-9 forms and SSNs collected via Telegram based exfiltration.
huntress.comwriteupAdded 3 Sep 2026, published 11 Mar 2026🛡️ Security - Fake Tech Support Delivers Havoc Command & Control
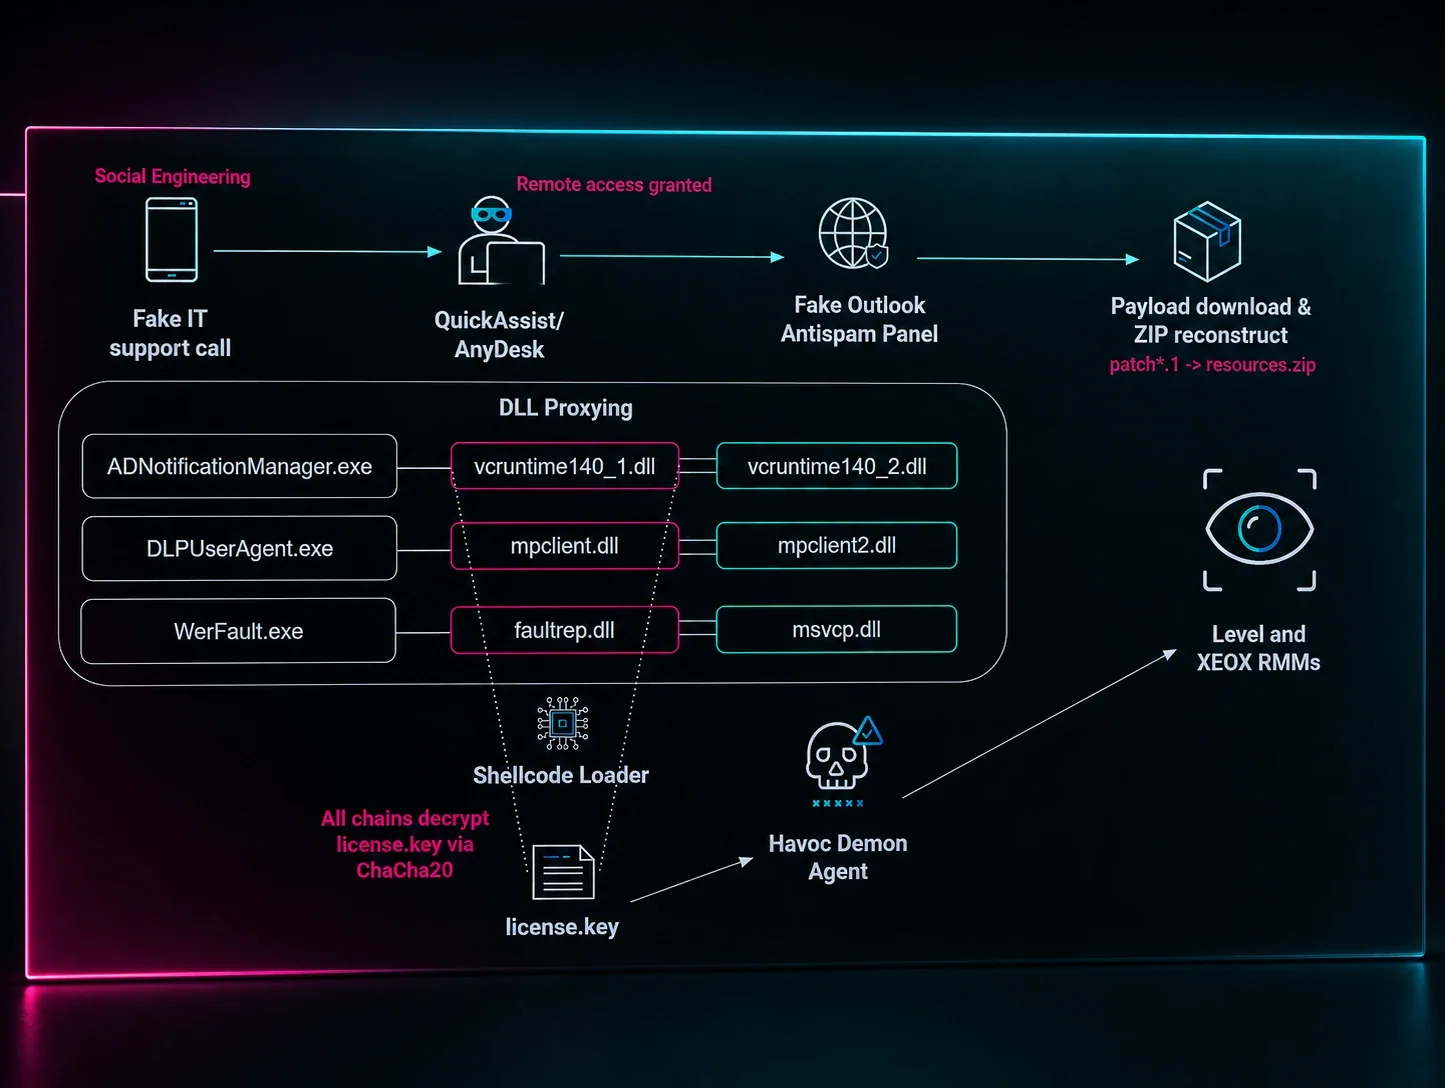
Huntress details a February 2026 intrusion cluster across five partner organizations combining fake tech support social engineering (spam bait, phone calls impersonating IT, QuickAssist/AnyDesk access, fake Outlook Antispam panel on AWS) with a customized Havoc Demon C2 agent using indirect syscalls, registry-based fallback C2, and DLL sideloading to evade EDR. Tradecraft overlaps with prior Sophos-documented Black Basta/FIN7 campaigns, suggesting affiliates or copycats reused the playbook; attackers reached nine additional endpoints within eleven hours, indicating likely ransomware/exfiltration intent.
huntress.comwriteupAdded 3 Sep 2026, published 2 Mar 2026🛡️ Security - The (!FALSE) Pattern | Huntress
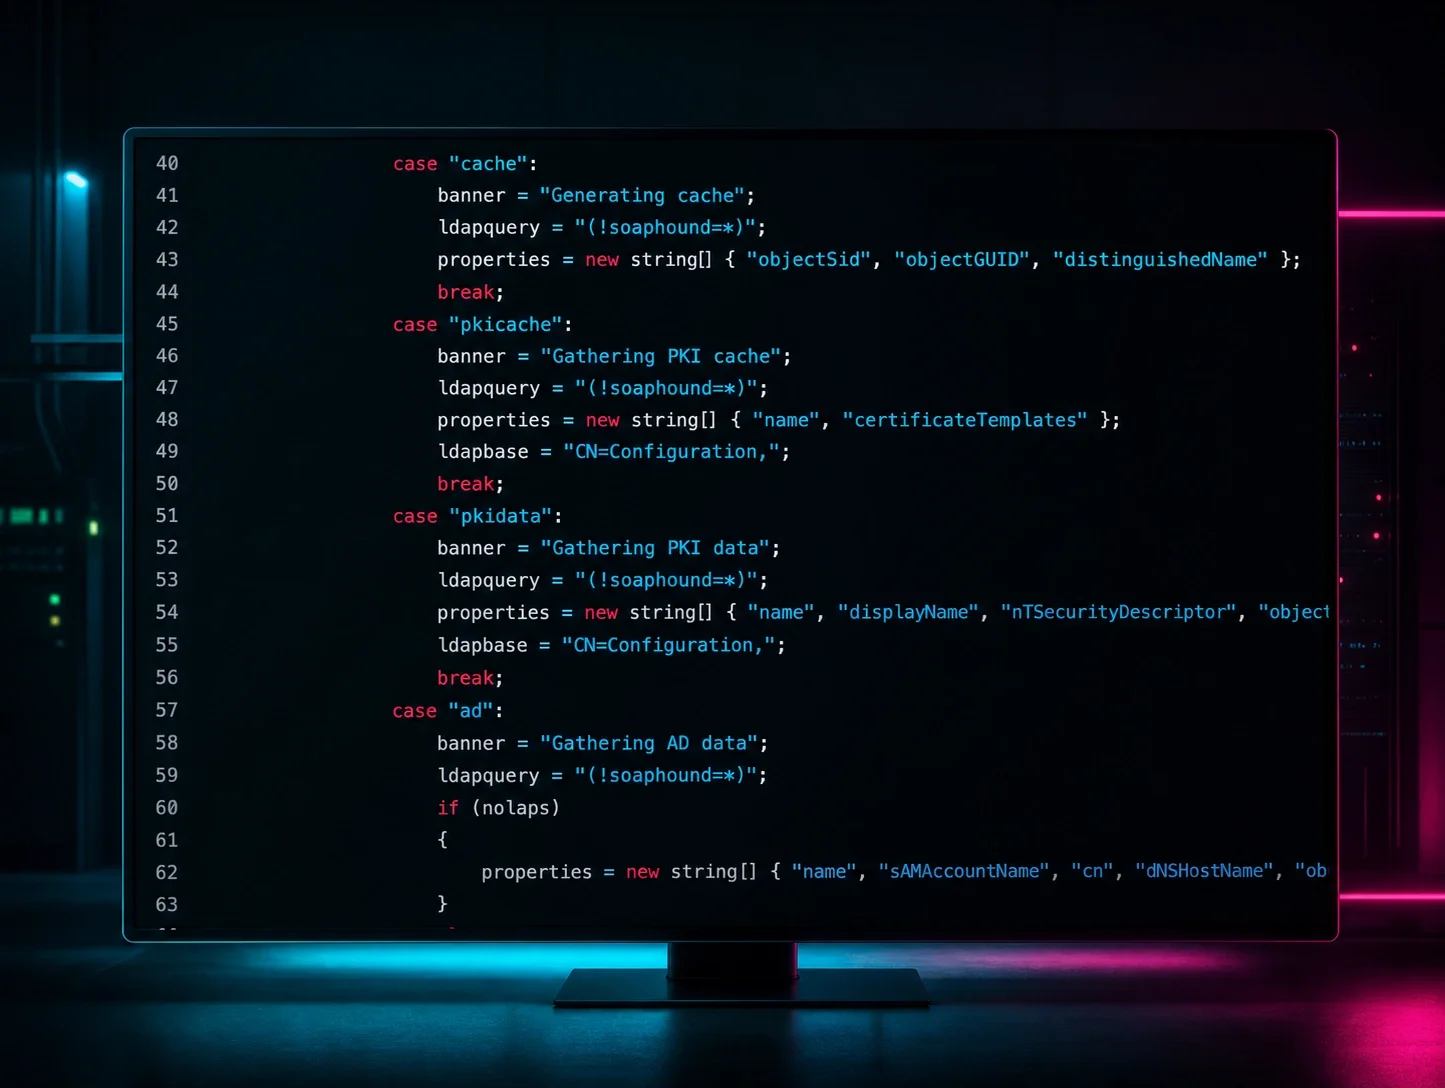
Part four of Huntress's LDAP/AD detection series shows that querying a non-existent LDAP attribute with negation (e.g., SOAPHound's hardcoded (!soaphound=*) filter) gets optimized by Active Directory's LDAP engine into (! (FALSE)) before it is written to Event ID 1644, erasing the tool's signature from logs. The author verifies this is universal AD behavior (not SOAPHound-specific), correlates it with SOAPHound's SDFlags:0x7 server control and its ADWS/port-9389 localhost proxying behavior, and publishes two Sigma rules combining the (! (FALSE)) pattern, attribute lists, and SDFlags for high-fidelity detection.
huntress.comwriteupAdded 3 Sep 2026, published 29 Jan 2026🛡️ Security - PeerBlight Linux Backdoor Exploits React2Shell CVE-2025-55182
Huntress details in-the-wild exploitation of CVE-2025-55182 ("React2Shell"), an unauthenticated RCE in React Server Components caused by insecure deserialization of the React Flight protocol's "thenable" chunk handling, affecting Next.js and other React-based apps. Post-exploitation payloads include PeerBlight (a musl-compiled Linux backdoor using BitTorrent DHT as fallback C2, sharing config-schema and XOR encryption traits with the Pink botnet and persistence code overlapping RotaJakiro), CowTunnel (an FRP-based reverse tunnel wrapping xfrpc for SOCKS5/TCP/HTTP/FTP/RDP proxying and a telnetd backdoor), ZinFoq (a Go post-exploitation implant with hex-encoded HTTPS C2, reverse PTY shells, and SOCKS5 pivoting), and a Kaiji botnet variant with hardware watchdog abuse. The piece includes detailed C2 protocol reversing (DGA algorithm, DHT config-distribution and RSA-signature verification) and dozens of observed C2/scanner IOCs across five real intrusion cases.
huntress.comwriteupAdded 3 Sep 2026, published 10 Dec 2025🛡️ Security - Oh my .. ! - Suspicious network traffic detected including Ransomware
A DFIR consultant walks through two Microsoft Defender for Endpoint high-severity "Ransomware" alerts that turned out to be benign inbound TCP SYN scans (ConnectionAttempt, not InboundConnectionAccepted) from an IP Microsoft had classified as malicious. The post shares KQL queries against DeviceNetworkEvents to identify internet-facing devices (via RemoteIPType and InboundInternetScanInspected), explains the difference between ConnectionAttempt and InboundConnectionAccepted ActionTypes, and stresses correlating with DeviceLogonEvents before concluding an alert is a false positive.
dfir.chwriteupAdded 3 Sep 2026, published 22 Jan 2025🛡️ Security - Today I Learned - Device Discovery
dfir.ch documents an incident response investigation where an NDR sensor flagged a suspicious internal port scan. The analyst used EDR telemetry to identify the responsible PowerShell script (hash-verified, Microsoft-signed) invoking Defender for Endpoint's Device Discovery feature (Scan-UdpTcpPorts, Scan-Vnc, Scan-WinRm, etc.), decoding its base64 ScannerArgs to reveal target IPs, MACs, and the CVEs it probes for (CVE-2021-44228, CVE-2022-22965). The scan turned out to be benign legitimate network discovery from Defender for Endpoint, explaining why it triggered an NDR false positive.
dfir.chwriteupAdded 3 Sep 2026, published 27 Apr 2024🛡️ Security