 Alpine Linux rebuilds GitLab after attempted RCE attack
Alpine Linux rebuilt its GitLab server and reset all passwords after attackers tried to exploit CVE-2026-97229, a maximum-severity integer overflow in the Onigmo regex engine bundled with Ruby, on October 20-21. Eight worker crashes occurred and four were partially successful. Missing logs and outbound connection records meant compromise could not be ruled out. Alpine had run GitLab 19.3.4, then 19.3.6, which lacked the Ruby patch; the fixed image is alpinelinux/gitlab:19.3.6 with Ruby 3.3.13.
 bleepingcomputer.comarticlePublished and added 1 Nov 2026🛡️ Security
- Prasenjit Sarkar (@stretchcloud) on X
Campfire is a free, open-source, self-hosted tool that runs Claude Code, Codex, Goose, Aider and OpenHands side by side in one browser tab. Each agent gets its own git worktree, with permission voting (30 second timer, majority rules), session replay, cross-backend agent races and a shared semantic memory layer. Installs with bunx the-campfire. The post also compares Clawboo, Conductor, Vibe Kanban and Crystl.
 x.comthreadAdded 1 Nov 2026, published 31 Oct 2026🧠 AI
 Appraisal by AI: Model-driven victim prioritization in the VOLTA infostealer
VOLTA (VOLTA-AUTODOXER) is a self-deleting Windows infostealer that, after theft and live session-based enrichment, POSTs an evidence bundle to OpenRouter so an LLM can rank the victim's assets by monetization value. It falls back across a Claude, Kimi and Gemini chain when a model refuses. Talos covers the builder model, the Chrome App-Bound Encryption bypass, the volta_debug.txt artifact and countermeasures such as blocking Chrome --headless.
 blog.talosintelligence.comwriteupPublished and added 31 Oct 2026🛡️ Security
- Bunny CDN Security Incident
Bunny CDN status-page notice, posted 28 October 2026, about unauthorized access at an infrastructure provider that hosted one bunny.net CDN node in Armenia. Traffic was stopped within 20 minutes and the server wiped. No access to the node was found, but cached content, Pull Zone configs and TLS certificates could have been exposed, so all platform certificates were reissued. Customers with their own certificates should rotate them with new private keys.
 status.bunny.netadvisoryAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
 [AINews] Building AIE CODE: The top Coding Agent Conference
AINews issue for 28 to 29 October 2026 from Latent Space. It opens with a preview of the AIE CODE summit (themes: Scaling without Slop, System One models, Increasing Ambition, with Jarred Sumner on Bun in Rust). It then recaps Twitter and Reddit news: Mistral Large 4 open weights (1.05T total, 52B active), Artificial Analysis benchmarks, Gemini 4 Carbon, Qwen4 rumours, Claude Code quota complaints and OpenAI frontier-run monitoring. Text was cut before the end.
 latent.spacearticlePublished and added 30 Oct 2026🧠 AI
 Rekt - News or Hype?
Rekt's "News or Hype?" compares four October 2026 AI headlines with their sources. These are Justin Drake's "bunker mode" ECDSA warning, Anthropic's Claude tracing NIST curve seeds to lrand48, OpenAI's agent spending Sepolia ETH from a default-mnemonic account, and Wiz's "AI uncovers" PHP RCE claim of 70% reach. It ends with four questions for checking claims.
 rekt.newsarticleAdded 30 Oct 2026🧠 AI
- Rekt - News or Hype?
Rekt News piece tracing three AI-security headlines back to their sources. It covers Justin Drake's October 2026 "bunker mode" warning about AI breaking ECDSA, OpenAI's report of a model spending Sepolia test ETH from a default developer mnemonic, and Wiz's "70% of the Internet" claim for PHP CVE-2026-109618 and CVE-2026-109619. It closes with four questions for checking a claim.
rekt.newsarticleAdded 29 Oct 2026🛡️ Security - Show HN: Auto Dismiss Mac OS "Allow <app> to find devices on local networks?"
dontallow is a two-file Swift launchd agent for macOS 15 and later that clicks "Don't Allow" on the "find devices on local networks" prompt. It watches the UserNotificationCenter process through an Accessibility observer, supports pause and allowlist, and can decode the Local Network rule store to show orphaned rows. It explains why Chromium temp-bundle paths make the prompt recur, and gives a PPPC profile route for fleets.
 github.comrepoAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 CVE-2026-98432: 9.8 CVE affecting all Ubuntu versions
CVE-2026-98432 is a Linux kernel use-after-free in the IPv4 TCP stack, tracked by Ubuntu (published 15 October 2026, updated 29 October 2026). ireq_opt/inet_opt were freed with plain kfree() while another CPU built a SYNACK under RCU, so ip_options_build() read freed memory; the fix uses kfree_rcu(). Ubuntu rates it High priority, CVSS v3.1 9.8 and v4.0 8.3. The page text does not list per-release package status.
 ubuntu.comadvisoryAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 Claude Code regularly sends each background agent’s transcript to its model
no-agent-summary.js is a roughly 70-line Bun preload by Flamerix AI that stops Claude Code from re-sending each background agent's full transcript to its model every ~30 seconds for a status-line summary. The write-up cites OpenTelemetry measurements of 18 to 26 percent of spend (since version 2.1.232), explains the setTimeout hook, and gives install and verify steps. It was tested on Linux with Claude Code 2.1.257 to 2.1.312.
 gist.github.comwriteupAdded 30 Oct 2026, published 29 Oct 2026🧠 AI
- GitLab Security Incident: Attempted Exploitation of CVE-2026-97229
Alpine Linux incident report on attempted exploitation of CVE-2026-97229 (CVSS 10.0), a regex-evaluation bug in Ruby's Onigmo engine reachable through GitLab CI configuration. An attacker crashed workers 8 times on 20 and 21 October 2026. Upgrading to GitLab 19.3.6 did not fix it because the patch sits in GitLab's bundled Ruby. Alpine rebuilt the instance and found no tampering with aports or releases.
 alpinelinux.orgwriteupAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security
- Managed for Malice: How Attackers Turn MDM into Remote Access
Huntress describes two incidents where attackers enrolled victims in attacker-controlled MDM tenants (Hexnode and Rippling) and used them to push ScreenConnect as SYSTEM. One began with a fake DocuSign MSI that bundled Hexnode; the other with a fake Teams calendar link leading to Rippling enrollment. Removing ScreenConnect did not stop reinstalls. The post lists IOCs, a detection chain and mitigations.
 huntress.comwriteupPublished and added 28 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CVE-2026-92885 is a critical (CVSS 3.1 9.8, CWE-287) authentication bypass in the Qode Membership WordPress plugin, versions through 2.0.6.2. A misspelled variable in the Facebook token-verification guard skips provider checks, so an unauthenticated attacker with a public nonce can get a session cookie for an existing account, including an administrator. The post gives the fix (2.0.6.3, bundled in Bridge 30.9), KEV/EPSS/SSVC status, and a SOC log-correlation and remediation plan.
x.comadvisoryAdded 31 Oct 2026, published 28 Oct 2026🛡️ Security  Malicious Firefox Extensions Impersonate Phantom, Jupiter, and Bitget to Steal Wallet Secrets
Socket analysis of three malicious Firefox add-ons impersonating Phantom, Jupiter and Bitget wallets, using Unicode homoglyph names. They steal seed phrases and private keys and send them to brand-named subdomains of bonto[.]io. The Phantom fake adds a runtime loader that fetches and evals a second stage, and bundles a drainer backend with Telegram forwarding. Includes IOCs, hashes and wallet addresses.
 socket.devwriteupPublished and added 27 Oct 2026🛡️ Security
 Backporting security fixes to stable releases
Trail of Bits argues that stable and LTS software, such as Ubuntu 26.04 LTS, Debian 13 and stable Linux kernel branches, carries many known CVEs that were fixed upstream but never backported. It measures the gap using the kernel CVE team's vulns.git (18 September 2026) and Debian and Ubuntu CVE feeds. Using Codex with GPT-5.6, the team got 142 fixes covering 90 CVEs applied to stable kernel trees and has begun sending patches to distributions.
 blog.trailofbits.comarticlePublished and added 27 Oct 2026🛡️ Security
- Prasenjit Sarkar (@stretchcloud) on X
Campfire is a self-hosted workspace by Prasenjit Sarkar that runs Claude Code, Codex, Goose, Aider and OpenHands side by side in one tab. Risky actions go through permission voting: a majority approves, any single deny blocks, and a 30 second timer ends the wait. Session replay shows which file or tool call triggered an action. The post cites Forever Security's report of a planted AGENTS.md. Codex followed it first time over 90% of the time and Claude Code about half the time. Try it with "bunx the-campfire".
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI  eMudhra, Brotli, and the Long Tail of a Security Fix
Socket post on why fixing the eMudhra weak-key intermediate CA incident (October 2026) and Brotli memory corruption CVE-2026-111497 takes more than updating Node.js. Bundled Brotli copies in Bun, Python Requests and .NET, Go binaries needing rebuilds, and per-program certificate stores all leave stale copies. It lists steps: track bundled components, keep a rebuild path, use workarounds, and verify the shipped artifact.
socket.devarticlePublished and added 26 Oct 2026🛡️ Security Node2Shell: Brotli Flaw Triggers Patching Across Microsoft, Node.js, Python Packages
CVE-2026-111497 (Node2Shell) is an out-of-bounds write in Google's Brotli decoder, versions 1.0.3 through 1.2.0, rated CVSS v4 9.2. Fixed in Brotli 1.0.10, 1.1.1 and 1.2.1, with patches from Node.js, Microsoft (.NET, Visual Studio, PowerShell on October 25), PyPI Brotli and brotlicffi, Bun, Envoy and Istio. Imperva showed code execution on Node.js 24.22.0 arm64; no in-the-wild exploitation is reported and some researchers say it only enables DoS.
 securityweek.comarticlePublished and added 26 Oct 2026🛡️ Security
 Broccoli2shell: Everything You Need To Know About The Critical Brotli Decoder Vulnerability
CVE-2026-111497 (Broccoli2Shell, also Node2Shell and HTTP2Shell) is an out-of-bounds write in the upstream Brotli C decoder. It affects Node.js, Bun, Envoy Proxy, Istio and Python packages, and can lead to memory corruption, information disclosure, crashes or RCE when untrusted Brotli data is decompressed. Wiz reports 91% of cloud environments have vulnerable resources. The post lists patching, inventory, rebuild and temporary mitigation steps.
 wiz.ioadvisoryPublished and added 25 Oct 2026🛡️ Security
 Brotlipocalypse
 is an OSM Security post (24 October 2026) on CVE-2026-111497, an out-of-bounds write in the google/brotli C decoder (1.0.3 through 1.2.0). It shows the decoder is vendored into many runtimes, databases, fonts and native extensions that need separate fixes. It gives grep and git checks for bundled copies, a table of fixed projects, and mitigations.
 opensourcemalware.comwriteupPublished and added 24 Oct 2026🛡️ Security
 Crypto's Two Answers to AI Bug Hunters
Bankless article on how crypto is responding to AI-driven bug discovery. It cites Bitcoin Core's 22 October 2026 policy change to fix and ship bugs findable with a simple LLM prompt instead of embargoing them, DefiLlama's 112 hacks over $1M in 2026 versus 70 in 2025, and the Initia exploit (~$2.7M). It contrasts an agility approach (Starknet, bunker mode) with minimalism and AI-assisted formal verification (Anthropic and Theorem proofs across 123 libraries).
 bankless.comarticlePublished and added 23 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CVE-2026-111497 is an out-of-bounds write in the Brotli decoder bundled with Node.js (CWE-787, CWE-252), rated CVSS v4.0 9.2 by the Google CNA and High by the Node.js project. Fixes are Node 22.23.4, 24.22.1 and 26.12.1, and 24.22.1 still labels Brotli 1.2.0 because the fix was cherry-picked. The post gives a SOC trail from input to worker, with remediation and verification steps. It notes no KEV match, CISA SSVC exploitation none, and only unverified public lab claims.
x.comadvisoryAdded 26 Oct 2026, published 23 Oct 2026🛡️ Security  eMudhra / emSign CA Compromise: What Python, pip, and CI/CD Users Need to Update
Guidance on the October 2026 eMudhra / emSign CA incident, where eight intermediate CA certificates had private keys generated with insufficient randomness. It explains why updating certifi alone does not fix pip's vendored bundle, and lists fixed versions (certifi 2026.10.19, pip 26.2.2, Python 3.15.1, 3.14.9, 3.13.17). StepSecurity's OpenSSL 4.0.3 tests showed the older bundle accepted seven emSign paths, while both corrected bundles rejected all fourteen.
 stepsecurity.ioarticlePublished and added 22 Oct 2026🛡️ Security
 PHP2Shell Exposure Depends on More Than Whether You Use PHP
Horizon3.ai post on assessing exposure to PHP2Shell (CVE-2026-109618, CVE-2026-109619), two memory-handling flaws in PHP. It says affected PHP may be bundled in third-party products, containers or managed hosting, and that finding it shows a remediation need, not proven exploitability. It lists questions to ask hosting providers and says Horizon3.ai has validated exploitation under specific preconditions that are still being characterized.
 horizon3.aiarticleAdded 29 Oct 2026, published 22 Oct 2026🛡️ Security
 Node2Shell: Node.js Brotli vulnerability allows remote code execution (CVE-2026-111497)
Node2Shell (CVE-2026-111497) is an out-of-bounds write in the Brotli decoder bundled with Node.js and Bun, triggered by malformed compressed input and rated high by Node.js, with possible remote code execution. Fixed in Node.js 22.23.4, 24.22.1 and 26.12.1 and Bun 1.4.4. The post covers exposure via Express 5, body-parser 2.x, fetch() and node:zlib, stopgaps, and a timeline with public proofs of concept on 22 October 2026.
 aikido.devadvisoryPublished and added 22 Oct 2026🛡️ Security
 eMudhra CA Compromise: The Trust Stores You Didn't Patch | Endor Labs
The eMudhra CA compromise (disclosed 20 October 2026) involves eight intermediate CA certificates whose private keys can be derived from the certificates themselves. They chain to AAA Certificate Services and three other roots. Browsers block them, but non-browser clients skip revocation and CT checks. Endor Labs finds 25 popular packages with frozen bundled root stores, 11 already patched, and gives a fingerprint-scanning script, test hosts and patch steps.
 endorlabs.comarticlePublished and added 21 Oct 2026🛡️ Security
 Your MCU likely escaped the eMudhra intermediate CA compromise
Analysis of the eMudhra intermediate CA compromise disclosed 20 October 2026, in which eight intermediate CA private keys were weak P-384 keys (top 376 bits zero, one key equal to 4) and publicly accessible. It explains web PKI chains and why browsers enforcing Certificate Transparency were not exposed. It argues MCU firmware that bundles only the single root it needs, as in Zephyr's HTTP GET sample, is likely safe unless it trusts an eMudhra or Sectigo cross-signing root.
 danielmangum.comarticleAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security
 LiteLLM 1.107.0 PyPI Wheel Contains a Credential Stealer and Persistent Python Backdoor
LiteLLM 1.107.0 macOS x86-64 PyPI wheel analyzed by OpenSourceMalware contains three injected files (cook.pth, cook.py, sitecustomize.py) that run on every Python start. The payload, called privcollect, steals browser, SSH, cloud, CI/CD and AI-tool credentials, then uploads an AES/RSA-encrypted bundle to www.litellm.dev/healthcheck. A forked loader also fetches domain.txt from GitHub and executes /codepy hourly. The post lists IOCs, hashes and remediation steps.
opensourcemalware.comwriteupPublished and added 21 Oct 2026🛡️ Security- eMudhra Intermediate CA Compromise
eMudhra Intermediate CA Compromise is a 20 October 2026 link-blog post reporting that private keys of eight eMudhra intermediate CA certificates were compromised. They chain to roots trusted by the Mozilla, Microsoft, Apple and Chrome programs. Software bundling trust lists needs updating: Linux distros must update ca-certificates, and uv 0.13.4, pip 26.2.2 and certifi 2026.10.19 ship new lists. The post does not describe how the keys were compromised.
 simonwillison.netarticleAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security
- Panos Gkatziroulis 🦄 (@ipurple) on X
Malvex (JoasASantos/Malvex) is an AI-driven malware analysis framework that integrates more than 30 analysis tools, a web REPL and an MCP server. Panos Gkatziroulis shared it on 19 October 2026 and noted that it was written by AI. The tweet gives no detail on which tools are bundled or how the AI drives them.
x.comrepoAdded 22 Oct 2026, published 19 Oct 2026🛡️ Security - MemTensor Compromise: Poisoned MemOS Releases on npm and PyPI
MemTensor MemOS compromise: three malicious versions of @memtensor/memos-cloud-openclaw-plugin on npm and MemoryOS 2.0.34 on PyPI (23 September 2026) bundled a Go binary, sckit, that harvested credentials and environment secrets and reported to skyleen.fr. The post gives OSV IDs, grep and find commands for exposure checks, safe versions (0.1.20, 2.0.33), rotation steps, and the missing gitHead as a provenance signal.
 safeguard.sharticleAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security
- AikidoSec/safe-chain
Aikido Safe Chain is an open-source local proxy and shell-alias wrapper for npm, yarn, pnpm, bun, pip, uv, poetry, pipx and pdm. It checks every package download, including deep dependencies, against the Aikido Intel malware feed and blocks malicious packages before install. It also enforces a configurable 48-hour minimum package age by suppressing too-new versions in registry metadata. It supports custom registries and a self-hosted malware-list mirror, and has CI/CD install recipes for GitHub Actions, Azure Pipelines, CircleCI, Jenkins, Bitbucket and GitLab.
github.comrepoAdded 17 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge CVE of the Day #080 covers CVE-2026-99999 ("PwnEscape"), a Linux kernel IPv4 checksum-completion flaw. Crafted checksum metadata can trigger a deferred write into an already-validated IPv4 header, which allows host memory disclosure from a guest or microVM over virtio-net and TAP. It gives upstream fixed branches (5.10.272 to 7.2.11), Amazon Linux, Red Hat and Ubuntu status, CVSS 9.3, EPSS 0.211% and a SOC investigation trail. No IOCs were verified.
x.comadvisoryAdded 19 Oct 2026, published 17 Oct 2026🛡️ Security - Romy (@0xBunny) on X
Tweet from 0xBunny announcing an update to Jev Workflows, an open-source workflow toolkit. It adds native Claude Code support alongside Codex, an opt-in Jev 1.14, experimental image/Box questions, shared QQ contract sync and local CI. Features were also mirrored to a sibling project called QQ. It is free, with no plugin quotas, and links to a GitHub repo.
x.comthreadAdded 17 Oct 2026, published 16 Oct 2026🧠 AI - 44er (@44errrr) on X
Announcement of hexvero, an MCP server that gives coding agents a static first look at binaries and app bundles across 18 formats (ELF, PE, Mach-O, APK, .NET, Go, Wasm, Electron, SQLite). It uses zero-dependency Node parsers and marks each finding confirmed or inferred with file and line. Its tool catalog is 3,043 tokens, against a claimed 509,696 for the established reverse-engineering MCP server. Paged output with a byte budget shrinks a 541 MB Electron app to a 15 KB result, 1.3 MB of JSON to 7.9 KB, and a 450 KB build diff to 1.2 KB. radare2, rizin or Ghidra plug in for disassembly, and `npx hexvero setup --apply` registers it with Claude Code, Cursor, Codex and 15 more clients. It is a concrete example of keeping MCP tool definitions and results small enough for an agent's context window.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026🧠 AI - 44er (@44errrr) on X
hexvero is a Node-only, zero-dependency MCP server that gives coding agents a static first-look triage of binaries and app bundles across 18 formats (ELF, PE, Mach-O, APK, .NET, Go, Wasm, Electron, SQLite). Findings are marked confirmed or inferred with file and line, and outputs are paged with a byte budget (a 541 MB Electron app yields a ~15 KB result). The author contrasts its 3,043-token tool catalog with a 509,696-token catalog of an established RE MCP server. radare2, rizin or Ghidra can be plugged in for disassembly, and setup registers it with Claude Code, Cursor, Codex and 15 more clients.
x.comtoolAdded 15 Oct 2026, published 14 Oct 2026🛡️ Security  Canonical Websites Disrupted in Second DDoS Attack This Year
SecurityWeek reports that Canonical's main web properties (ubuntu.com, canonical.com, the Ubuntu blog and developer site, and the security advisory pages and API) were hit by a sustained DDoS attack confirmed on October 8. Downtime was a little over four hours. Launchpad and the Snap Store appeared unaffected. The attack's size and origin are undisclosed and nobody has claimed it. It follows a more disruptive April attack that took down Launchpad and the Snap Store and was claimed by The Islamic Cyber Resistance in Iraq – 313 Team. It is unclear whether the two are linked.
securityweek.comarticlePublished and added 12 Oct 2026🛡️ Security How Zcash Plans to Hide Your Keys From AI and Quantum Attacks
Decrypt reports that Zakura, which builds a Zcash full node, expects post-quantum signature opcodes in Zcash in January, to enable hash-based signatures for transparent pools. The plan rotates to a fresh transparent address after every transaction so public keys stay hidden, and adds a WOTS hash-based backup signature. Private information retrieval, shipping this week in the Vizor wallet, stops servers from linking the rotated addresses. It follows Justin Drake's "bunker mode" warning that AI-driven math could break ECDSA. The plan covers only transparent payments, and no activation date has been confirmed.
 decrypt.coarticlePublished and added 11 Oct 2026🛡️ Security
- sepehr071/iran-mcp
iran-mcp is an open-source catalog of 39 MCP servers (488 tools) that let AI agents query Iranian websites such as Digikala, Torob, Divar, Snappfood, Jabama, Paziresh24, TSETMC and qavanin.ir, with prices normalised to Toman. Most servers are unofficial, read-only Python packages run with uvx; three are official hosted servers. It ships Claude Code plugins, Agent Skills, bundles, proxy lists and a machine-readable servers.json.
github.comrepoAdded 24 Oct 2026, published 11 Oct 2026🧠 AI - Dan Kornas (@DanKornas) on X
Arcjet JS SDK is an Apache-2.0 JavaScript monorepo that adds runtime security checks to AI apps, agents and HTTP endpoints. It ships framework SDKs (Next.js, Node.js, Bun, Deno, Fastify, NestJS) plus a Guard API for agent tool calls, MCP handlers, queue workers and background jobs that have no HTTP request object. Features include prompt injection detection, sensitive-information detection (PII, credit cards, custom patterns) and token-bucket, fixed-window and sliding-window rate limiting.
x.comrepoPublished and added 11 Oct 2026🛡️ Security - Dan Kornas (@DanKornas) on X
Arcjet JS SDK is an open-source (Apache-2.0) JavaScript monorepo that adds runtime security to AI apps, agents and HTTP endpoints. It ships request SDKs for Next.js, Node.js, Bun, Deno, Fastify and NestJS. It also has a Guard API for places with no HTTP request object, such as agent tool calls, MCP handlers, queue workers and background jobs. Built-in checks cover prompt-injection detection, sensitive-information detection (PII, credit cards, custom patterns) and token-bucket, fixed-window or sliding-window rate limits, including token budgets.
x.comrepoPublished and added 11 Oct 2026🧠 AI  Zcash developers set January target for quantum-resistant payments after ‘bunker mode’ scare
Zcash developer Roman Akhtariev, writing for the Zakura client team, announced a January target for adding post-quantum signature opcodes supporting hash-based signatures to Zcash's transparent (public) payment pool, which holds about 70% of issued ZEC. The move responds to Ethereum researcher Justin Drake's "bunker mode" warning that AI could soon break the elliptic-curve math behind Bitcoin and Ethereum wallet keys. Zakura has also built a private-information-retrieval balance-lookup tool, now experimentally available in the Vizor wallet, that lets a wallet check address balances without revealing to the server which addresses are linked, separate from the shielded-pool quantum-recovery work still needed to defend against store-now-decrypt-later attacks.
 coindesk.comarticlePublished and added 9 Oct 2026🛡️ Security
 The OpenSourceMalware Show #24
Weekly OpenSourceMalware podcast episode discussing three fresh supply-chain attacks: the Tensorlake AI-agent SDK compromised via a preinstall-triggered Mini Shai-Hulud-derived worm (setup.mjs + math_symbol.js, run via Bun) that steals credentials; a Contagious Interview-style attack where a cloned GitHub repo drops a malicious .npmrc pointing npm install at a Chinese mirror (npmmirror.com) to resolve a hidden package; and 42 malicious RubyGems published by "Ghost Dev" that typosquat/brandjack crypto tooling, sleep 20–40 minutes via extconf.rb to evade detection, then either open a reverse shell or deploy a Python-based "Wallet Guard" crypto-theft kit targeting TronLink, MetaMask, Phantom, Binance, Coinbase, Trust Wallet, Exodus, and Electrum. The hosts also discuss multi-package "combined payload" evasion and how AI-driven slopsquatting is making cross-ecosystem typosquats more effective.
opensourcemalware.comtalkPublished and added 9 Oct 2026🛡️ Security Coinbase Cryptographer Calls Drake's 'Bunker Mode' Warning 'The Very Definition of FUD'
News piece reporting that a Coinbase cryptographer dismissed Justin Drake's proposal for Ethereum validators/users to adopt a 'bunker mode' against AI-accelerated cryptanalysis as unfounded FUD. Vitalik Buterin weighed in that AI-accelerated math risk is real but should be pointed at lattice-based cryptography rather than elliptic-curve schemes like ECDSA used by Ethereum, while a former Ethereum Foundation researcher argued bunker mode would not help if the curves actually broke.
 thedefiant.ioarticlePublished and added 8 Oct 2026🛡️ Security
 Vitalik Buterin backs crypto ‘bunker mode’ amid rapid AI math advances
Ethereum researcher Justin Drake, backed by Vitalik Buterin, warns that rapid AI progress in mathematics (citing OpenAI's recent batch of math findings and a 10,000-agent solve of Navier-Stokes) could break ECDSA-based wallet signatures before quantum computers ever do, and that lattice-based post-quantum schemes may not be safe either. They recommend a controlled 'bunker mode' migration of crypto holdings to fresh addresses whose public keys have never been exposed on-chain, while cautioning that botched migrations carry their own risk.
 cointelegraph.comarticlePublished and added 8 Oct 2026🛡️ Security
 Vitalik Flags AI Risk to Crypto, Warns Against Rushed Wallet Moves
Vitalik Buterin responds to Ethereum Foundation researcher Justin Drake's bunker mode proposal, agreeing AI-accelerated cryptanalysis could break ECDSA, the signature scheme behind most crypto wallets, in months not years, and that lattice-based schemes like ML-DSA billed as quantum-safe could also take serious hits within two years. Buterin gives practical key-hygiene advice such as keeping funds in addresses that never exposed a public key and rotating multisig signer keys after every operation with offchain signature collection, while warning that botched migrations cost more than hacks.
bankless.comarticlePublished and added 8 Oct 2026🛡️ Security Will AI Break Crypto Encryption? Ethereum’s Vitalik Buterin Weighs In on 'Bunker Mode' Shift
Decrypt reports on Ethereum co-founder Vitalik Buterin's warning that AI-driven advances in mathematics could plausibly break lattice-based cryptography within two years, a day after Ethereum Foundation researcher Justin Drake urged the industry to adopt "bunker mode" — moving funds to addresses whose public keys have never been exposed. The piece covers pushback on reusing public keys, the tradeoff between quantum-resistant lattice schemes (used by projects like Cardano) and their potential AI-math vulnerability, and Buterin's preference shift toward hash-based cryptography, with commentary from BIP-360 co-author Isabel Foxen Duke and Charlie Quant Lab's Ananda Banerjee urging calm preparation over panic.
decrypt.coarticlePublished and added 8 Oct 2026🛡️ Security Tensorlake npm Package Compromised to Spread Shai-Hulud Worm
The tensorlake npm package, version 0.5.144 released 8 October 2026, carried a new Shai-Hulud worm variant, per Aikido's analysis. A preinstall script runs node lib/setup.mjs, downloads Bun and launches lib/Math_Symbol.js, which steals cloud, CI/CD, SSH, Vault, browser and crypto-wallet secrets. It reaches C2 iseekaigogo[.]com or an Ethereum smart-contract dead drop, and has a wipe dead-man's switch tied to a GitHub token.
 cybersecuritynews.comarticleAdded 19 Oct 2026, published 8 Oct 2026🛡️ Security
 Morning Minute: Ethereum Researcher Says AI May Break Crypto Encryption Before Quantum
A daily crypto-market newsletter segment reporting Ethereum Foundation researcher Justin Drake's warning that AI, not quantum computing, may be the first to break ECDSA — the elliptic-curve signature scheme securing Bitcoin and Ethereum — potentially within months by recovering private keys from exposed public keys using large GPU clusters. Drake calls for industry-wide "bunker mode": migrating self-custodied funds to fresh addresses whose public keys remain hashed/hidden, and names exchanges (Binance, Bitbank, Robinhood, Bitfinex, Tether) he wants to harden cold storage. The article also notes a concurrent Europol report flagging crypto wallets with already-revealed public keys as the main weak point for future quantum/AI attacks, since those cannot be retroactively protected.
decrypt.coarticlePublished and added 8 Oct 2026🛡️ Security Bitcoin and ether holders urged to enter ‘bunker mode’ against possible AI attacks
Ethereum researcher Justin Drake and co-founder Vitalik Buterin warn that rapid AI progress in mathematics could break the elliptic-curve signatures securing Bitcoin and Ethereum wallets within months - far sooner than quantum computers are expected to - urging large holders to enter bunker mode by migrating funds to addresses whose public keys have never been exposed onchain. Buterin also flags that lattice-based post-quantum schemes, the basis of NIST's signature standard, could face similar AI-driven erosion, pushing Ethereum's long-term roadmap toward hash-based signatures instead. The piece grounds the warning in already-documented AI-assisted exploit discovery: a 5-year-old Coldcard hardware-wallet firmware bug drained over 1,367 BTC, BTCPay Server Lightning-node thefts, Core Lightning bugs surfaced via AI-generated audits, and Anthropic's demonstration of AI models writing working exploits against simulated DeFi contracts.
coindesk.comarticlePublished and added 8 Oct 2026🛡️ Security AI risk to crypto wallets: Ethereum researcher warns keys could be cracked in months
Ethereum Foundation researcher Justin Drake warned on October 7, 2026 that advances in AI and mathematics could break ECDSA — the signature scheme securing blockchain transactions — within months, potentially letting an attacker recover a private key in about a week using a large GPU cluster. He urged gradual "bunker mode" preparation rather than panic: rotating funds into fresh addresses whose public keys have never been exposed on-chain, strengthening cold storage, and accelerating Ethereum's move toward hash-based signature schemes such as SPHINCS for critical signers like oracles and L2 security councils.
 en.cryptonomist.charticlePublished and added 8 Oct 2026🛡️ Security
 tensorlake NPM package compromised with Shai Hulud worm
Aikido details a new Shai-Hulud worm wave that compromised the tensorlake npm package (v0.5.144, 100k+ lifetime installs) via a hijacked GitHub maintainer identity. The malware's preinstall script drops the Bun runtime to run an obfuscated payload that exfiltrates CI/cloud secrets, browser crypto-wallet extension data (via a bundled HackBrowserData binary), uses a blockchain dead-drop (an Ethereum contract queried via public RPC nodes) to resolve a fallback C2, and includes a GitHub-token-triggered dead-man's switch that wipes infected machines. The post includes full IOCs: file hashes, the C2 domain iseekaigogo[.]com, and the threat actor's wallet/contract addresses.
aikido.devwriteupPublished and added 8 Oct 2026🛡️ Security Justin Drake Urges 'Bunker Mode' Migration to Fresh Crypto Addresses
Justin Drake urges migrating to fresh crypto addresses over AI cryptographic break fears; Ledger CTO disputes the risk of mass migration.
thedefiant.ioarticlePublished and added 8 Oct 2026🛡️ Security Tensorlake npm Package Compromised: A Worm With a Hostage Token That Wipes Your Machine If You Revoke It
StepSecurity details how tensorlake@0.5.144 was pushed to npm after malicious commits landed directly on the tensorlakeai/tensorlake GitHub repo's main branch under a maintainer's identity, carrying a valid npm provenance attestation despite being malicious. The preinstall hook downloads Bun to run an obfuscated payload that steals GitHub/npm tokens, cloud and Vault/Kubernetes secrets, SSH keys, browser logins, and AI-tool configs (Claude, Cursor, Windsurf), then self-propagates by republishing stolen npm packages and committing persistence files (.claude/settings.json, .vscode/tasks.json) to reachable repos. A "hostage token" mechanism installs a gh-token-monitor service that runs a home-directory wipe if the stolen GitHub token is revoked before the monitor is removed, inverting the normal incident-response order.
stepsecurity.iowriteupPublished and added 8 Oct 2026🛡️ Security- Port of the TypeScript compiler, checker and lsp to Rust, by LLM
ts-rust (npm package tsc-rs) is a from-scratch Rust port of Microsoft's TypeScript compiler/checker/language server (typescript-go), produced almost entirely by LLM coding agents rather than hand-written. The author first spent over $400,000 in API tokens running GPT-5.6 Sol and GPT-6 Astra in long agentic '/goal' loops, which wrote 1.3M lines of Rust but plateaued at ~84% compatibility; switching to Claude Opus 5.5 produced a working version in 10 hours and, after ~$24,000 of further API spend over two weeks, reached 100% compatibility on tested real-world projects while passing all 181,711 ported Go baseline tests. Benchmarks show the Rust port running about 1.6x faster than the Go tsc 7 compiler (though slower than Bun's native `bun check`) across dozens of open-source codebases including VS Code, TanStack Query, Sentry and T3 Code.
github.comrepoPublished and added 8 Oct 2026🧠 AI  Ethereum Researcher Says AI May Break Encryption Before Quantum Does
Ethereum Foundation researcher Justin Drake warns that AI-driven mathematical advances could break ECDSA — the signature scheme securing Bitcoin and Ethereum — before quantum computers do, potentially recovering a private key from an exposed public key in about a week using a large GPU cluster. He calls for "bunker mode": a controlled mass migration of funds to fresh addresses whose public keys have never been exposed, urges major custodians (Binance, Bitbank, Robinhood, Bitfinex, Tether) to harden cold storage, and pushes Ethereum to accelerate its move to hash-based (post-quantum) cryptography.
decrypt.coarticlePublished and added 7 Oct 2026🛡️ Security Improving SPIRE security and resiliency with AWS managed services
AWS Security Blog walkthrough on hardening SPIRE (the SPIFFE Runtime Environment) in production by replacing its default self-managed components with AWS managed services: AWS KMS for SVID signing keys, Amazon Aurora PostgreSQL as the datastore, AWS Private CA as the upstream certificate authority, Amazon S3/CloudFront for trust bundle distribution, AWS Secrets Manager for delivering SVIDs to serverless/container workloads, and Amazon Verified Permissions (Cedar policies) for fine-grained SPIFFE-ID-based authorization. It addresses operational concerns like key custody, datastore resiliency, PKI integration, and offline identity validation, and links to a GitHub reference deployment and a SPIFFE/SPIRE-on-AWS workshop.
 aws.amazon.comarticleAdded 7 Oct 2026, published 6 Oct 2026🛡️ Security
- Show HN: OpenChart – OSS TradingView alternative with your own AI agent
OpenChart is an open-source TradingView-style desktop charting app (Electron, Node.js/Bun, Effect runtime) that embeds AI agents into statistical/technical analysis, real-time market alerts and agentic opportunity research. It ships a custom DSL called Tea (inspired by TradingView's Pine Script) for writing indicators, and a conversation interface built on assistant-ui and the AG-UI event protocol so users converse with agents while charting.
github.comrepoPublished and added 6 Oct 2026🧠 AI  Active Supply Chain Attack: Malicious node-ipc Versions Published to npm
StepSecurity's AI Package Analyst detected three malicious node-ipc versions (9.1.6, 9.2.3, 12.0.1) published simultaneously on May 14, 2026 by a rogue/compromised maintainer account, injecting an 80KB obfuscated IIFE into the CommonJS bundle that harvests 90+ credential file categories (AWS, Azure, GCP, SSH, Kubernetes, GitHub, Claude AI/Kiro configs, Terraform, etc.) and exfiltrates them via HTTPS and raw DNS TXT queries to a typosquatted Azure-mimicking C2 domain. The writeup includes a full stage-by-stage technical teardown (daemonization, SHA-256 targeting gate on 12.0.1, custom base-16 nibble-reversed obfuscation, dual-channel exfiltration) plus file hashes, network IOCs, and remediation guidance for developers and CI/CD pipelines.
stepsecurity.iowriteupAdded 5 Oct 2026🛡️ Security Register Codex's Computer Use as a Claude Code MCP Server
A thread shows how to register Codex's built-in Computer Use capability — the "cua_repl" MCP server found in ~/.codex/plugins/cache/openai-bundled/unified-computer-use/ — as a custom user MCP server (named "codex-cu") inside Claude Code, letting Claude drive Mac GUI automation via Codex's computer-use backend instead of a separate CUA driver. The author reports an informal benchmark across 8 computer-operation tasks: Claude Opus 5.5 + Codex Computer Use scored 6/8, Codex alone scored 6/8, and the original CUA driver only scored 3-4/8, with a caveat that future Codex updates could break this cross-agent MCP reuse.
x.comthreadPublished and added 5 Oct 2026🧠 AI SunsetSyntax (@sunsetsyntax) on X
A short account of switching from a split Neo4j (relationships) + separate vector DB (embeddings) setup — which required manually reconciling IDs whenever an agent wrote a fact — to NornicDB, a single Go-based graph+vector store that speaks Bolt/Cypher and bundles an MCP server in one process. The point is that agents can query a unified memory store without an app layer babysitting two separate databases.
x.comthreadPublished and added 4 Oct 2026🧠 AI Sujeet (@sujeetgholap) on X
A tweet arguing that Meta is using the credibility it earned from releasing open-weights Llama models to legitimize Muse, a free-as-in-beer service that bundles compute, weights, and apps rather than offering genuine open access. The commentary frames this as a strategic pivot from open-weights advocacy to a closed, Meta-controlled ecosystem play, explaining why Muse feels less aligned with the open-source AI movement than Llama was.
x.comthreadPublished and added 3 Oct 2026🧠 AI- pwasm 0.2a0
Simon Willison describes pwasm, a pure-Python WebAssembly engine he originally vibe-coded in January, and how he later let Claude Opus 5.5 work on it autonomously with minimal prompting: over 42 commits the model extended it to handle almost all of the WASM spec and got working builds of MicroPython, QuickJS and Micro QuickJS running inside it, bundled in the PyPI wheel. He frames it as a rough but telling illustration of how much more capable today's coding agents are than the models used ten months earlier, while still not trusting the alpha-tagged result.
simonwillison.netarticleAdded 8 Oct 2026, published 1 Oct 2026🧠 AI - Dan Kornas (@DanKornas) on X
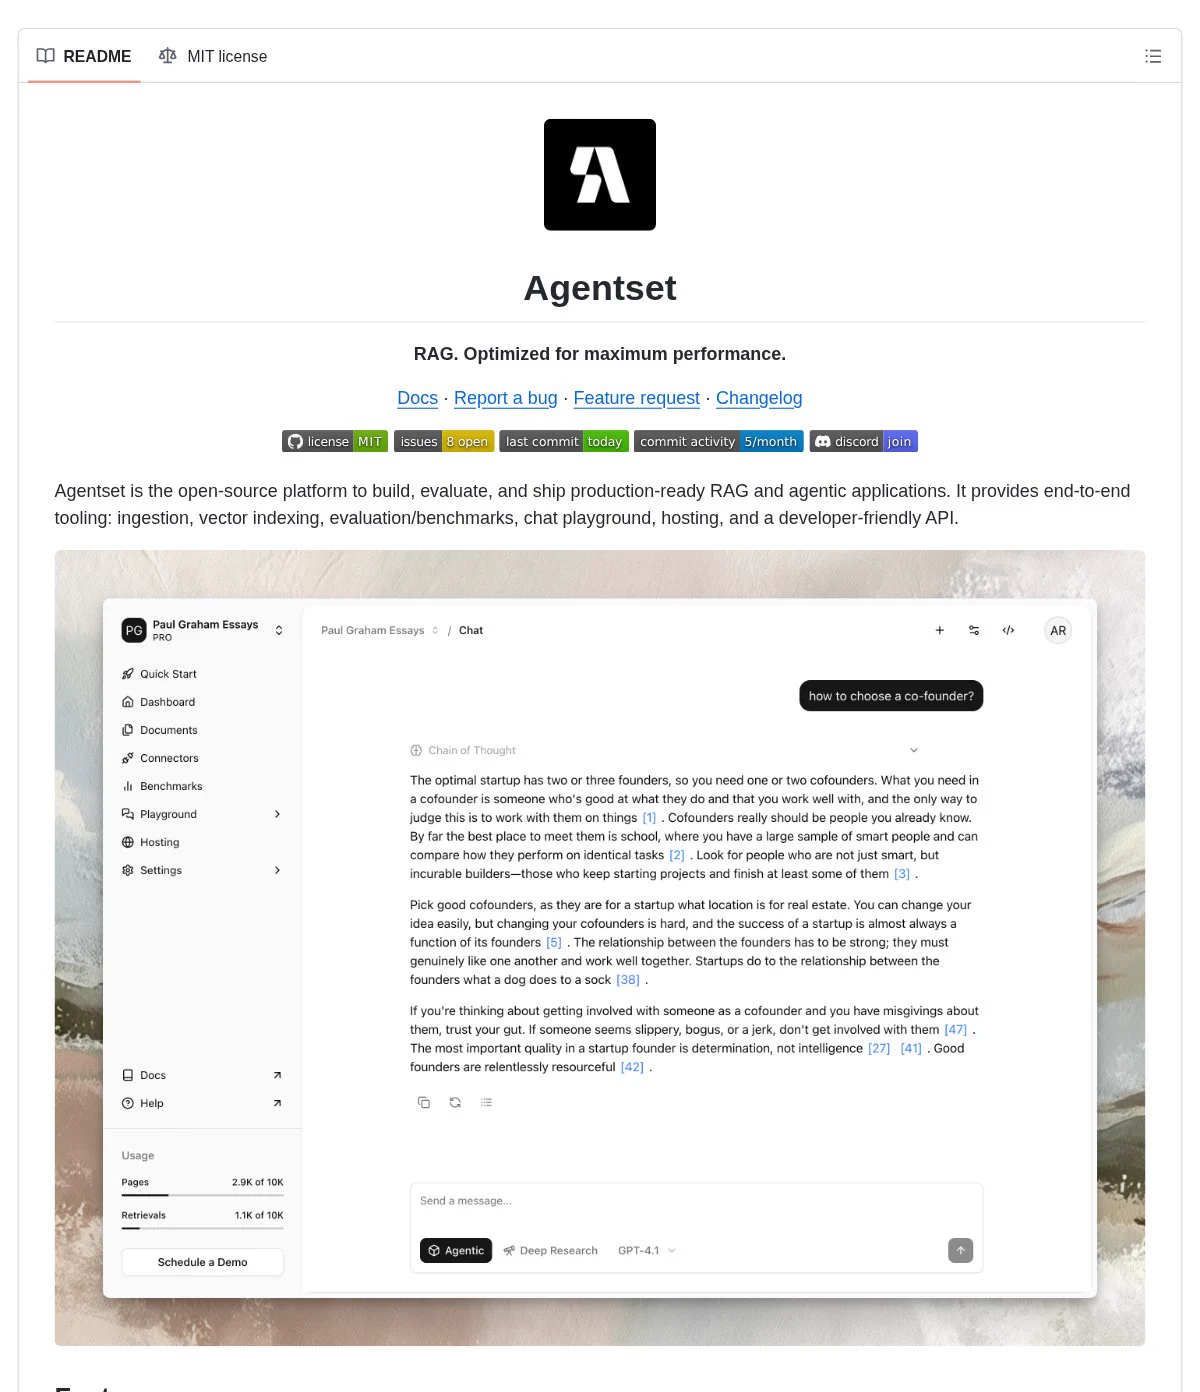
Agentset is an open-source (MIT-licensed) platform for building RAG and agentic applications, bundling ingestion, chunking, embeddings, retrieval, vector indexing, a citation-aware chat playground, evaluation/benchmark tooling, and a deployment layer (hosting, preview links, custom domains, typed SDKs, OpenAPI spec) into one codebase. It lets builders choose their own LLM, embedding model, and vector database rather than locking into a single stack.
x.comthreadPublished and added 1 Oct 2026🧠 AI  MALFEX npm Attack Spreads Windows RAT, Steals Discord and Browser Data
CloudSEK's Global Threat Intelligence team uncovered MALFEX, a supply-chain campaign active since August 2023 that uses malicious npm packages (including tlxbnhd, tldriver, mxdriver, img-to-native, cdn-img-fetch, function-flag, function-color) to deliver malware on Windows. One chain disguises a Windows executable as a PNG to load Overlord RAT, an open-source Go-based RAT that uses the Solana blockchain to resolve C2 addresses; a second chain fetches a 64MB Node.js bundle that steals Discord tokens, browser cookies/credentials, crypto wallets and Telegram session data, exfiltrating via a Discord webhook. Some malicious packages stayed live for over a year even after related packages were pulled or flagged.
 hackread.comarticleAdded 3 Oct 2026, published 30 Sep 2026🛡️ Security
- Launch HN: Magnitude (YC S25) – Self-optimizing inference engine for agents
Magnitude is an open source local inference engine (Apache 2.0) that compiles and tunes its GPU/CPU kernels on the user's exact device before a model runs, claiming up to 2x faster decode than llama.cpp (92% faster on Metal, 19% on CUDA) with 27% lower memory per agent. It ships as a cross-platform desktop app with a bundled CLI and an OpenAI-compatible API, offering one-click connections to agent tools like Pi, OpenCode, Hermes, Codex, OpenClaw, Claude Code, and Cline, running fully offline on Apple Silicon, NVIDIA, AMD, or CPU-only hardware.
github.comrepoPublished and added 30 Sep 2026🧠 AI - Trail of Bits (@trailofbits) on X
Announcement tweet for Trail of Bits's September "Tribune" newsletter, which fact-checks 1Password's AI-powered patching benchmark, details a signature-forgery bug found in Miden's zkVM and a string-slicing bug in the Lean theorem prover/language, and reports 27 advisory submissions to OpenClaw plus seven new completed security reviews. It links out to the full newsletter on Mailchimp (mailchi.mp/trailofbits).
x.comthreadAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security - Average AI Bro (@AverageAiBro) on X
Claude Code added a `claude --desktop` command that opens the Desktop app on the current directory or a resumed/continued session, plus `claude plugin configure` to view a plugin's options. Bundled .mcpb MCP servers can now have their settings set at `plugin install --config` time so they start immediately without a manual Configure step. The post also notes CLAUDE_CODE_DISABLE_WEB_FETCH to disable WebFetch and an allowedProviders setting to restrict which API providers a managed machine can use.
x.comthreadPublished and added 30 Sep 2026🧠 AI - Determined Attacker Uploads Malicious Webshells to Parks and Rec Management Platform Servers
Huntress details a four-act intrusion against a shared parks-and-recreation management platform running on IIS, where an attacker first tried noisy unauthenticated exploits (IIS 8.3 tilde enumeration, WebDAV verb abuse, upload-handler bypasses) before simply registering a member account and uploading .aspx webshells via a member-file upload feature across three servers. The attacker enumerated hosts, extracted web.config/connection strings, hunted for cardholder data (Fortis/MXMerchant webhook logs, CVV/card-number strings), then escalated to timestomping, re-deploying known-filename webshells, and finally injecting an AI-generated PowerShell/JS dropper into a trojanized jQuery file to turn site visitors' browsers into WebRTC/WebSocket C2 clients (ririmochii/bubuneeko Cloudflare Workers infrastructure). Includes a zh-CN PowerShell user-agent string used for attribution and full command/IOC listings useful for detection engineering.
huntress.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security  OpenAI Gave AI Agents Their Own Computers at DevDay 2026. Here's Everything It Announced
Roundup of OpenAI DevDay 2026 announcements: Dots, always-on cloud hosted agents running on GPT-6 Astra and the newly open sourced Codex harness that connect to thousands of apps; GPT-6.1 Sol, a workhorse model priced at one fifth of Astra tokens while nearly matching it on agentic coding and computer use; and Ultrafast, a premium speed tier up to 8x faster in Codex on Cerebras hardware, bundled with a new Pro 500 plan. Also covers a shared human plus agent workspace called ChatGPT Space, a fast fixed choice Decisions API, Codex Security Cloud for scheduled repo vulnerability scanning and patching, an Agents API adding computer use and multi agent context compaction tooling, Private Intelligence with zero data retention and confidential computing inference coming this fall, and marketplace and plugin features such as Sign in with ChatGPT and OpenAI Marketplace.
decrypt.coarticleAdded 30 Sep 2026, published 29 Sep 2026🧠 AI upm Launches as a Fast, Tiny Package Manager Written in TypeScript
Socket covers upm, a new ~250KB TypeScript package manager built by Nuxt/Nitro/UnJS creator Pooya Parsa that uses only Node.js built-ins for fast npm installs and exposes a JavaScript API for embedding in other tools. Its security-relevant defaults include disabling dependency lifecycle install scripts and enforcing a one-day minimum release age before selecting new package versions (both configurable), aimed at mitigating malicious install-script and fresh-release supply-chain attacks; it also lacks hoisting and can read (but has limited compatibility with) npm, pnpm, and bun lockfiles.
socket.devarticlePublished and added 29 Sep 2026🛡️ Security- 0xtbug/Recat
Recat is a local, Bun-based web workspace for reviewing security findings, including ones produced by AI agents such as Hermes, Codex and Claude Code. It reads a folder of finding.json, README and PoC evidence per project, and offers a dashboard by severity, status and asset coverage (web, smart contract, mobile, desktop, network, hardware). It also has filters by vulnerability class, an evidence viewer, JSON and ZIP exports, password-protected access with a censored view, and a SKILL.md reporting skill that lets agents write findings straight to the source folder.
github.comrepoAdded 16 Oct 2026, published 27 Sep 2026🛡️ Security - Agent Control Standard (ACS)
Agent Control Standard (ACS) is an OWASP GenAI Security Project specification that lets a separate Guardian Agent inspect an AI agent's proposed actions before they execute and return allow/deny/modify/ask/defer over an authenticated JSON-RPC wire, with OpenTelemetry/OCSF audit trails and a CycloneDX/SPDX/SWID AgBOM inventory. The reference implementation runs Microsoft's Agent Governance Toolkit (AGT) behind the ACS contract with Bun, including host shims for Claude Code and OpenCode, and demonstrably denies a destructive `rm -rf /` command from a live coding-agent session while allowing benign ones. The project is explicit about current gaps — the wire is unauthenticated (issue #70) and the reference Guardian fails open by default (issues #32/#37) — and only 2 of 16 lifecycle hooks are evaluated live in v0.1.0.
github.comrepoAdded 26 Sep 2026🛡️ Security  Progressive Skill Discovery as Access Control for Tool-Using LLM Agents
Introduces "skilder," a framework that bundles LLM agent capabilities into roles (skills, tools, instructions, and limits) delivered progressively through a single MCP server, so an agent starts with a minimal catalog and only gains tool access as it learns the roles a task requires. This structural approach enforces access control deterministically at the server layer rather than relying on prompt-based policy, addressing context bloat and governance gaps in enterprise tool-using agents. Evaluated against flat-context tool selection and multi-agent orchestration across 13 tasks and six models, showing zero unauthorized tool calls or parameter violations when agents completed the discovery protocol.
 arxiv.orgpaperAdded 26 Sep 2026🧠 AI
 Researchers Detail DifyTap Flaws in Dify That Could Expose AI Chats Across Tenants
Zafran Security disclosed four vulnerabilities (dubbed DifyTap) in the open-source agentic workflow platform Dify, including two critical authorization bypass/path-traversal bugs (CVE-2026-41947, CVE-2026-41948) letting attackers redirect app traces to an attacker-controlled LLM provider or reach Dify's internal Plugin Daemon API, plus two file-preview authz flaws (CVE-2026-41949, CVE-2026-41950) exposing other tenants' uploaded documents and chat files via UUID guessing. Separately, Dify's file-parsing stack bundled a version of PDFium vulnerable to CVE-2024-5846, a use-after-free that can trigger heap corruption via a crafted PDF. All but CVE-2026-41948 were patched in Dify 1.14.2.
 thehackernews.comarticleAdded 26 Sep 2026🛡️ Security
 Socket Joins New OpenJS Program to Fund Node.js Security Work
Socket announces it is an inaugural funder of the OpenJS Foundation's new Security Stewardship Program, which pools money to pay both bug bounty researchers and maintainers doing triage, patching, and backporting for Node.js, starting there before expanding across the JS ecosystem. The article frames this against a broader funding crisis: curl suspended its bounty program after AI-generated report floods, GitHub restructured its bounty tiers, Canonical moved Ubuntu kernel updates to weekly releases to keep pace with rising CVE volume, and Node.js paused bounty payouts in April after the Internet Bug Bounty pulled funding, even as HackerOne report volume to the Node.js team spiked 4.6x in one month.
socket.devarticlePublished and added 25 Sep 2026🛡️ Security Finding Gadgets Like It's 2026 (Atredis Partners)
Atredis Partners built an LLM-driven pipeline (WALA/ASM call-graph builder, a FastAPI graph query server, Claude Code as the reasoning/validation agent, and a dynamic test/debug runner) to automate discovery of Java deserialization gadget chains against modern, hardened application servers (WebSphere, WildFly, Payara). The project found 17 confirmed chains, 6 novel, including CB1-Shaded-RCE — a chain that bypasses JPMS's TemplatesImpl restrictions via a shaded/relocated copy of Xalan's XSLTC shipped inside WildFly's JSTL jar, giving RCE on the latest WildFly on JDK 21 — plus a novel JNDI-injection chain in Payara via AttributeComparator/InjectableJMSContext. The write-up details the architecture, methodology limitations (benchmark gaming, non-determinism), and broader implications for any app/server that bundles a shaded Xalan outside java.xml, with tooling released on GitHub (atredispartners/llmchainhunter).
 atredis.comwriteupAdded 25 Sep 2026🛡️ Security
 Re-Enabled GitHub Actions Expose Thousands of Repositories to Mini Shai-Hulud
Socket reports that the actions-cool/issues-helper and actions-cool/maintain-one-comment GitHub Actions, compromised in the May 2026 Mini Shai-Hulud campaign and disabled by GitHub, were re-enabled on September 16, 2026 with their release tags still pointing to the malicious code. Any workflow referencing them by tag (about 15,000 dependents for issues-helper alone) resumed running the Bun-executed obfuscated payload. Workflow run logs show the switch from fast "Repository access blocked" failures to multi-minute successful runs. The post gives remediation: SHA-pin actions, rotate secrets, and hunt for oven-sh/setup-bun and bun run index.js in runner logs. An update says both repos were disabled again on September 25.
socket.devwriteupPublished and added 24 Sep 2026🛡️ Security Discovering and exploiting a remote code execution vulnerability in OpenCode (GHSA-632h-h47v-g4x4)
GHSA-632h-h47v-g4x4 is an RCE in OpenCode's /global/upgrade endpoint, fixed in 1.18.22. The target value reached `npm install -g opencode-ai@TARGET`, so an attacker could supply a malicious tarball URL with a preinstall script. A text/plain HTML form bypassed CORS through top-level navigation because the handler parsed JSON without checking Content-Type. Affects 1.14.30 to 1.18.21 installed via npm, pnpm or Bun.
 securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 24 Sep 2026🛡️ Security
 MemTensor npm and PyPI Packages Compromised in Credential-Stealing Supply Chain Attack
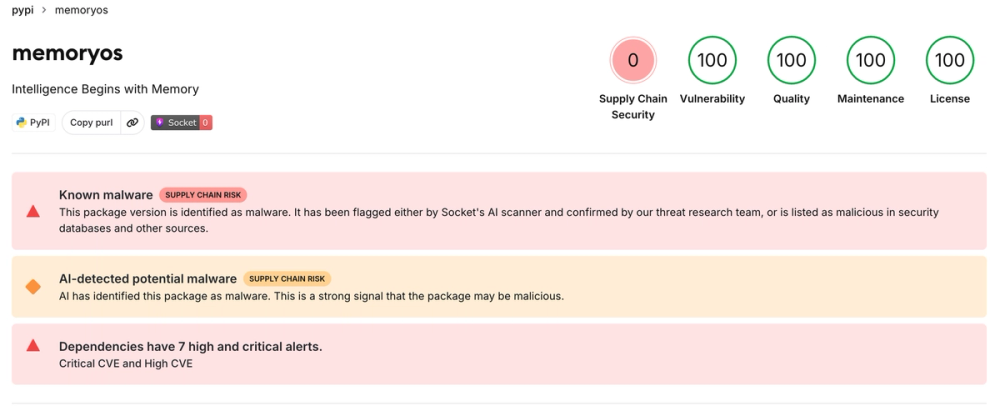
Socket details a supply-chain compromise of MemTensor's MemOS packages: npm package @memtensor/memos-cloud-openclaw-plugin (versions 0.1.21, 0.1.23, 0.1.25) and PyPI package MemoryOS (2.0.34), both published as the latest release on their registries. Each malicious release bundles a stripped, statically-linked Go binary called sckit that launches on import/plugin-load, scans $HOME for npm, PyPI, GitHub, GitLab, AWS, Vault and SSH credentials, and exfiltrates them to C2 servers under skyleen[.]fr, with the npm variant also capturing OpenClaw agent prompt text and the code additionally showing potential worm-like republish capability using stolen registry tokens.
socket.devwriteupPublished and added 23 Sep 2026🛡️ Security Containers Are No Longer a Security Boundary (CVE-2026-80521)
Depth First researchers detail CVE-2026-80521, a Linux kernel use-after-free in the AF_UNIX subsystem's garbage collector (a race between edge visibility during SCM_RIGHTS sends and vertex freeing in unix_del_edge/unix_walk_scc_fast), discovered with their in-house AI vulnerability-detection model dfs-large1 and used to win a Google kernelCTF slot. They released a working container-escape exploit against the latest Ubuntu 26.04, plus a second exploit for CVE-2026-52910 against Ubuntu 24.04, arguing that AI-accelerated bug discovery has broken the assumption that shared-kernel containers (Docker/Kubernetes, nsjail, Firejail, Bubblewrap) provide a hard security boundary, and recommending migration of sensitive workloads to microVM isolation like Firecracker or Kata Containers.
 depthfirst.comwriteupAdded 26 Sep 2026, published 22 Sep 2026🛡️ Security
- antonio-morales/Fuzzing101
Fuzzing101 is a hands-on course/repo by antonio-morales with 10 exercises targeting real software projects to teach coverage-guided evolutionary fuzzing using AFL++ (a fork of lcamtuf's AFL). It covers core fuzzing concepts like seed mutation, coverage feedback, and crash triage, with exercises tested on Ubuntu 20.04 and a provided VM image, making it a practical on-ramp for finding real vulnerabilities via fuzzing.
github.comcourseAdded 22 Sep 2026🛡️ Security - MichaelKinsy/PiG
PiG reimplements Pi — a minimal, extensible terminal coding agent — as a single native Go binary with no Node.js dependency, while remaining behaviorally pinned to a specific Pi release (0.87.1) and running Pi's TypeScript extensions unchanged. It adds a multi-language extension host (Go, Rust, Python, Node), a "Piglet" mechanism for bundling extensions/skills/prompts into a named shareable agent, and a formal parity-tracking process (PORT_MAP.md, DIVERGENCES.md, coverage reports) that documents every intentional divergence from the upstream Pi reference implementation.
github.comrepoAdded 27 Sep 2026, published 17 Sep 2026🧠 AI - Copy Fail (CVE-2026-31431): 9-year-old Linux kernel LPE found by Theori's Xint Code
A GitHub repository from Theori's Xint Code team detailing CVE-2026-31431, a Linux kernel local privilege escalation bug ("Copy Fail") that had gone undetected for roughly nine years. The researchers confirmed exploitability across current production kernels including Ubuntu 24.04 LTS (6.17.0-1007-aws), Amazon Linux 2023 (6.18.8-9.213.amzn2023), RHEL 10.1 (6.12.0-124.45.1.el10_1), and SUSE 16 (6.12.0-160000.9-default).
github.comrepoAdded 17 Sep 2026🛡️ Security - Markakd/Container_escape
A GitHub repository hosting target-specific proof-of-concept exploits for two Linux kernel vulnerabilities, CVE-2026-52910 and CVE-2026-80521 (the latter an AF_UNIX kernel bug also documented in a kernelCTF LTS exploit-chain submission), both usable to break out of container isolation. The project ships a QEMU/Docker-based disposable VM builder (pinned to specific Ubuntu cloud images and kernel versions) so the destructive PoCs can be compiled and detonated only inside throwaway guests rather than on real hosts.
github.comrepoAdded 2 Oct 2026, published 16 Sep 2026🛡️ Security - Shai-Hulud-2.0-Detector — npm supply-chain compromise scanner
Shai-Hulud-2.0-Detector is a GitHub Action and CLI tool that scans package.json/lockfiles for packages compromised in the Shai-Hulud 2.0 (Nov 2025) and ChainDrop (Aug 2026) npm supply-chain worms. It uses semver-precise matching against a database of 1,241+ known-compromised package versions (auto-updated daily from Datadog and Wiz Research feeds) to flag malicious preinstall/postinstall droppers (setup_bun.js, Math_Symbol.js), rogue GitHub self-hosted runners named SHA1HULUD, and ChainDrop's new IDE-persistence hooks in .claude/settings.json and .vscode/tasks.json. It ships SARIF output for GitHub Security tab integration, an allowlist system, and a detailed incident-response guide covering credential rotation and forensic checks.
github.comrepoAdded 16 Sep 2026🛡️ Security  Securing the unpatchable in an age of AI-driven vulnerabilities
Cisco Talos argues that AI-accelerated vulnerability discovery is outpacing organizations' ability to patch, especially for unpatchable operational technology (OT) like medical devices and industrial control systems. It recommends network-level compensating controls instead of patching: upstream next-generation firewalls with intrusion prevention for virtual patching, VLAN/ACL-based micro-segmentation to restrict which devices can reach legacy systems, and visibility into legacy network fingerprints to build an asset inventory. It also debunks the air-gap myth, citing WannaCry's spread through unpatched Windows XP in the NHS as a cautionary example of "hope for the best" failing.
blog.talosintelligence.comarticleAdded 7 Oct 2026, published 16 Sep 2026🛡️ Security- shinthink/blitzstrike
Blitz Strike is an open-source Model Context Protocol server (TypeScript/Bun) that packages a structured 3-tier pentesting methodology — BLITZ (attack-surface recon), EAGLE-EYE (source-to-sink reachability tracing), and STRIKE (live validation before reporting) — into callable tools any MCP client (Claude Code, Cursor, Gemini, etc.) can drive with a single run_engagement call. It ships 130 self-written security tools, 317 indexed tool manuals, 58 data-driven escalation chains with negative-control checks, a Web3/Solidity audit module with Foundry proofs, and a regression/benchmark suite (453 checks, reported 1.0 detection / 0 false-positive rate) to make every finding verified rather than pattern-matched.
github.comrepoAdded 2 Oct 2026, published 12 Sep 2026🛡️ Security - agent-egress-bench
Agent Egress Bench is an open, tool-neutral benchmark maintained by PipeLab (makers of Pipelock) that tests whether products mediating an AI agent's outbound traffic — proxies, egress firewalls, MCP wrappers, agent gateways — actually catch exfiltration attempts caused by prompt injection or misalignment, rather than testing the underlying model itself (that's left to AgentDojo, InjecAgent, CyberSecEval, AgentHarm, ASB). It ships a reproducible Go runner with a proxy/WebSocket/MCP/A2A adapter contract, an offline validator, DSSE-signed evidence bundles, and a CI-runnable GitHub Action, and separates containment from false-positive rate as two distinct scored axes with immutable case IDs and OWASP Agentic Top 10/MITRE ATT&CK mappings. Its governance explicitly permits third parties to publish results unfavorable to the maintainer's own Pipelock product.
github.comrepoAdded 12 Sep 2026🛡️ Security  Why OVAL Feeds Outperform NVD for Linux Vulnerability Management | Blog | Endor Labs
Endor Labs explains why OVAL (Open Vulnerability and Assessment Language) feeds from Linux distributions like Debian, Ubuntu, and Red Hat produce more accurate vulnerability data than NVD for container/Linux scanning. Using CVE-2022-1587 (PCRE2 DoS) as a case study, it shows how NVD rated the flaw "Critical" (CVSS 9.1) while Ubuntu's OVAL-based advisory rated it "Low" because the distro had already backported a fix into a version string (10.34-7ubuntu0.1) that naive NVD-based scanners would still flag as vulnerable.
endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security








Showing 90 of 182
Show more