Skip to content

508 results for “MCP”

What you seeeverything
“MCP”
x.comthread🧠 AI

Lonnie VanZandt (@lonniev) on X

Secure Courier is a consent flow in Tollbooth DPYC, a monetization network for paid MCP services, that lets an AI agent act for a Nostr npub without holding the user's nsec. The service sends a signed, sealed direct message over Nostr relays, the user replies with a signed approval and an expiry, and the service issues its own encrypted grant. Lonnie VanZandt presents it as an alternative to central identity providers and CIBA. The thread gives no audit results.

Model Context ProtocolNostrOAuth+2
Secure CourierExcalibur-MCPLonnie VanZandt

mcp, agents· Added 1 Nov 2026

x.comtool🧠 AI

zahT3 (@zahT3zuo) on X

Hotseat is a free, open-source macOS menu bar app that moves Claude Code and Claude Desktop to another of the user's Claude accounts in one click and returns to the same session. Sessions, settings, skills and MCP servers are shared, so `claude --resume` works under either account. When a session hits a usage limit, it offers to continue under another account. It never reads tokens or cookies. Install with Homebrew.

Claude CodeClaude DesktopmacOS+2
HotseatAnthropic

coding-agents· Added 1 Nov 2026, published 31 Oct 2026

x.comthread🛡️ Security

Tanmay (@TanmayK_03) on X

DBHub, a database MCP server, had a read-only mode bypass in its SQL check. The check treated every `--` as a comment, but MySQL only starts a comment when whitespace follows it. A hidden write statement could therefore still run, and a prompt injection could trigger it. Fixed in version 0.22.6. Replies say enforcement belongs in database grants and that parser tests need to be dialect-specific.

DBHubMySQLModel Context Protocol
prompt injection

AppSec, AI Security· Added 31 Oct 2026, published 30 Oct 2026

x.comthread🛡️ Security

Lonnie VanZandt (@lonniev) on X

Tollbooth DPYC's "Secure Courier" is a consent scheme that lets an AI agent act for a Nostr npub at a paid MCP service without holding the user's nsec. The service sends a signed, sealed Nostr direct message, the user replies signed with their nsec and sets an expiry, and the service issues its own grant. The thread contrasts this with central identity providers and CIBA, arguing a breach reaches only grants that service issued.

Model Context ProtocolNostrOAuth+1
Tollbooth DPYCSecure CourierCIBA+4

Identity & Access, AI Security· Added 1 Nov 2026, published 30 Oct 2026

github.comrepo🧠 AI

rikugan: LLM reverse-engineering agent for IDA Pro and Binary Ninja

Rikugan is a reverse-engineering agent that runs inside IDA Pro and Binary Ninja. It has its own generator-based agent loop, context management, plan mode and 60+ tools, and does not depend on an external MCP server. An orchestrator spawns parallel subagents to analyze a binary. It supports Anthropic, Gemini, MiniMax, Kimi, OpenAI-compatible endpoints and Ollama, with per-model notes.

IDA ProBinary NinjaHex-Rays+6
RikuganClaude Opus 4.6Claude Sonnet 4.6+6

agents, coding-agents· Added 30 Oct 2026

github.comrepo🛡️ Security

rikugan: LLM reverse-engineering agent for IDA Pro and Binary Ninja

Rikugan is an open-source reverse-engineering agent that runs inside IDA Pro 9.0+ and Binary Ninja, with its own agent loop instead of an MCP server. It has 60+ tools (decompiler, xrefs, strings, types, IL/microcode), parallel subagent exploration, an experimental /modify natural-language patching command and an experimental Binary Ninja deobfuscation skill for control flow flattening and opaque predicates. It supports Claude, Gemini, MiniMax, Kimi, OpenAI-compatible endpoints and Ollama.

IDA ProBinary NinjaLLM+3
control flow flatteningopaque predicatesMBA expressions+1

Malware & RE, AI Security· Added 30 Oct 2026

x.comtool🧠 AI

Ritik Shukla (@Retik_S) on X

kanzo is a local kanban board that coding agents can update. It ships as one 4 MB binary that starts in 2 ms and runs on localhost. It also works as an MCP server, so Claude Code and Codex see the same tasks as the user. The board is stored as a folder that can sync through a private git repo. The post is brief and gives no further detail.

Model Context ProtocolClaude CodeCodex+2
kanzo

mcp, coding-agents· Published and added 30 Oct 2026
x.comthread🧠 AI

aiproduck (@aiproduck) on X

Ruflo is an MIT-licensed wrapper for Claude Code and Codex that adds agent swarms, vector memory and an MCP server. The plugin install writes no files to the workspace, while npx init adds a .claude/ directory, CLAUDE.md and hooks. The post warns that mods run with the account's permissions, so users should read them first. It gives no benchmarks or architecture detail.

Claude CodeCodexModel Context Protocol+1
Ruflo

coding-agents, agents, mcp· Published and added 30 Oct 2026

vulncheck.comtool🛡️ Security

VulnCheck - Outpace Adversaries

VulnCheck Open Source is an index of VulnCheck's open-source tooling for its vulnerability and exploit intelligence. It lists a Python API client, a CLI, a GitHub Action for CI/CD, go-exploit (a Go exploit framework), an MCP server for delivering intelligence to AI clients, and VulnCheck Insights, a Chrome extension that highlights CVEs, CPEs and PURLs on web pages and enriches them. The page gives only one-line descriptions.

GoPythonGitHub Actions+2
VulnCheckgo-exploitVulnCheck Insights+2

Offensive Security, DevSecOps· Added 29 Oct 2026
pillar.securityarticle🛡️ Security

SAIL Framework: A Practical Guide for AI Security

The SAIL Framework from Pillar Security is a seven-phase, lifecycle-oriented method for securing AI systems. The phases are AI policy and safe experimentation, AI asset discovery, AI security posture management, AI red teaming, runtime guardrails, sandboxed execution for agents and MCP servers, and AI activity tracing. It argues for a "Shift Up" approach that protects the business logic AI controls, and it is meant to sit on top of existing standards.

Model Context Protocol
SAIL FrameworkPillar Securityprompt injection+3

AI Security, GRC· Added 29 Oct 2026

x.comthread🧠 AI

Prasenjit Sarkar (@stretchcloud) on X

A thread on Cloudflare's agent-readiness scan and the AgentReady.org open spec for "Agent Experience", developed with Vercel, Stripe, Auth0, Mintlify, Google, Netlify and Elementor. The scan grades whether agents can find a site (robots.txt, DNS), read clean Markdown, pass bot rules, and discover an MCP server or API catalog. One quoted example raised a score from 20 to 67 by shipping an API catalog with Link headers, an MCP server card, a skills index and an AI catalog file.

Model Context ProtocolCloudflareMarkdown
AgentReady.orgOraNick Launches+7

mcp, agents· Added 30 Oct 2026, published 29 Oct 2026

x.comthread🛡️ Security

Rohan Paul (@rohanpaul_ai) on X

Rohan Paul's X post summarizes a TikTok paper on MCP attacks. LLM agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the user query, the server reply and the final answer. The attack works because agents read natural-language tool descriptions when choosing and ordering tool calls. The visible text is truncated and gives no success rates or defenses.

Model Context ProtocolLLM
tool poisoningdata exfiltration

AI Security· Added 30 Oct 2026, published 29 Oct 2026

github.comcourse🧠 AI

rohitg00/ai-engineering-from-scratch

ai-engineering-from-scratch is a free, MIT-licensed curriculum of 542 lessons in 20 phases, from math and deep learning through transformers, LLM engineering, MCP, agents and capstones. Code is in Python, TypeScript, Rust and Julia. It includes three graded projects (retrieval evaluation, agent trace debugger, tool call firewall), installable tutor skills for Claude Code and Codex, and certification prep tracks.

PythonTypeScriptRust+13
Rohit GhumareOpenClawHermes+6

· Added 29 Oct 2026

securityweek.comarticle🛡️ Security

Cisco Open Sources Quarry to Catch AI Agent Attacks Hidden in Harmless Steps

Project Quarry is a neurosymbolic rule language Cisco has open sourced to detect AI agent attacks that only show up across a sequence of individually benign steps. Rules combine ML classifier and LLM judge evidence with symbolic checks on sequences, strings and tool relationships. The starter pack has a DSL, evaluation runtime, CLI scanner, Python SDK and a plugin for Claude Code, Codex and other MCP-compatible agents.

QuarryModel Context ProtocolClaude Code+2
Project QuarryCisco Integrated AI Security & Safety Framework

AI Security, Blue Team & Detection· Published and added 29 Oct 2026

endorlabs.comarticle🧠 AI

What is an AIBOM? AI bill of materials explained for security teams | Endor Labs

An AIBOM is a machine-readable inventory of models, datasets, dependencies, AI services, agents and MCP servers, with evidence of origin, license, integrity and evaluation. The Endor Labs explainer walks through a worked CycloneDX example for a fine-tuned support assistant. It compares CycloneDX ML-BOM, SPDX 3.x, the OWASP AIBOM project and the May 2026 CISA/G7 guidance, and lists what an AIBOM cannot show: runtime behavior and agent actions.

CycloneDXSPDXSBOM+5
Endor LabsOWASPCISA+3

ai-policy, ai-infra· Published and added 29 Oct 2026

endorlabs.comarticle🛡️ Security

What is an AIBOM? AI bill of materials explained for security teams | Endor Labs

AIBOM explainer from Endor Labs: an AI bill of materials is a machine-readable inventory of models, datasets, dependencies, AI services, agents and MCP servers, with origin, license and integrity evidence. It walks through a CycloneDX entry for a fine-tuned model, compares CycloneDX ML-BOM, SPDX 3.x, the OWASP AIBOM Generator and the May 2026 CISA/G7 minimum-elements guidance, and lists a six-step build process. It also states what an AIBOM cannot show: model safety, runtime behavior and coding-agent actions.

CycloneDXSPDXSBOM+2
EU AI ActISO/IEC 42001CISA+5

Supply Chain, AI Security, GRC· Published and added 29 Oct 2026

x.comthread🛡️ Security

Rohan Paul (@rohanpaul_ai) on X

Rohan Paul's X post summarizes the paper "Log-To-Leak: Prompt Injection Attacks on Tool-Using LLM Agents via the Model Context Protocol", from TikTok researchers. It reports that MCP-using agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the query, server reply and final answer. The attack works through natural-language tool descriptions that agents read when choosing and ordering tools. The visible text is truncated.

Model Context ProtocolLLM
Log-To-Leakprompt injectionTikTok+1

AI Security· Added 29 Oct 2026, published 28 Oct 2026

x.comthread🧠 AI

Eddy (@ieddysun) on X

Expo's official skills package gives AI coding agents scoped instructions for building Expo apps. One command, npx skills@latest add expo/skills --skill '*', installs it for Cursor, Copilot and Windsurf, while Claude Code and Codex use their plugin marketplaces. Skills include expo-router, expo-animation, expo-upgrade and eas-update. The Expo MCP server adds live docs lookup, compatible dependency installs, EAS build monitoring and simulator screenshots.

ExpoReact NativeExpo Router+9

coding-agents, prompting, mcp· Added 29 Oct 2026, published 28 Oct 2026

x.comthread🛡️ Security

Hakimi Eiqbal (@hakimieiqbal) on X

A practical reverse-engineering map by hakimieiqbal on X that picks tools by target: native binaries, .NET, Electron, iOS, firmware, WebAssembly and network protocols. It introduces REA (morluto/rea), which connects coding agents to RE tools, and lists MCP bridges for IDA Pro, Ghidra and radare2. It adds an evidence-first workflow and free courses such as pwn.college and OpenSecurityTraining2.

GhidraIDA Proradare2+3
REAFlare-OnOpenSecurityTraining2+5

Malware & RE, Learning· Added 29 Oct 2026, published 28 Oct 2026

x.comthread🧠 AI

Hakimi Eiqbal (@hakimieiqbal) on X

A thread by Hakimi Eiqbal that maps reverse-engineering tools by target type: native binaries, Electron, .NET, iOS, firmware, WebAssembly and network protocols. Its AI sections cover REA (an open-source layer connecting coding agents to analysis tools) and MCP bridges for IDA Pro, Ghidra and radare2. It argues for an evidence-first workflow and gives a prompt that separates verified facts from hypotheses.

Model Context ProtocolClaude CodeCodex+8
REAIDA Pro MCPGhidrAssistMCP+3

coding-agents, mcp· Added 29 Oct 2026, published 28 Oct 2026

endorlabs.comarticle🧠 AI

ADLC compliance: Mapping agentic development to NIST SSDF, OWASP, and the EU AI Act | Endor Labs

ADLC compliance is Endor Labs' interpretation of how NIST SSDF (SP 800-218), the OWASP LLM and Agentic Top 10 lists, and the EU AI Act apply to software built with coding agents. It splits requirements into a code surface and an action surface (shell, files, MCP calls, package installs). It gives a four-step EU AI Act scoping path and says that system prompt rules and agent self-reports are not audit evidence.

CursorClaude CodeModel Context Protocol+3
Endor LabsNISTOWASP+3

ai-policy, coding-agents· Published and added 28 Oct 2026

endorlabs.comarticle🛡️ Security

ADLC compliance: Mapping agentic development to NIST SSDF, OWASP, and the EU AI Act | Endor Labs

ADLC compliance guide from Endor Labs that maps agentic development to NIST SSDF (SP 800-218 v1.1), the OWASP LLM Top 10 2025 and Agentic Top 10, and the EU AI Act as amended by Regulation (EU) 2026/1744. It splits controls into a code surface and an action surface (shell, file access, MCP calls, package installs). It gives a four-step AI Act scoping path, the new Annex III date of 2 December 2027, and evidence guidance. It states the crosswalk is the vendor's interpretation, not legal advice.

Endor LabsModel Context ProtocolClaude Code+3
NIST SSDFNIST SP 800-218NIST SP 800-218A+13

GRC, AI Security, Supply Chain· Published and added 28 Oct 2026

endorlabs.comarticle🛡️ Security

The ADLC maturity model: 5 stages of agentic development security | Endor Labs

The ADLC maturity model is a proposed five-stage framework from Endor Labs for scoring security controls over coding agents, from unmanaged experimentation to continuous verification. Each stage has requirements on two tracks, agent actions (shell commands, MCP calls, package installs) and agent output (code, dependencies, secrets). It sets stage 3 at deterministic hooks that block actions, gives evidence-based assessment questions, and lists traps such as relying on prompt-level rules.

Endor LabsAURIModel Context Protocol+2
ADLC maturity modelOWASP SAMMOWASP Top 10 for LLM Applications+5

AI Security, GRC, DevSecOps· Published and added 28 Oct 2026

x.comthread🧠 AI

Kizuno18 (@Kizuno18) on X

Kizuno18's X post argues that the move from local stdio and Docker MCP servers to remote HTTP/SSE endpoints matures the Model Context Protocol in enterprise infrastructure. It lists three trade-offs: short-lived OAuth/JWT bearer tokens replace mounted admin credentials, deferred tool discovery avoids roughly 20k tokens of eager schema loading, and HCP Terraform enforces Sentinel/OPA policy, audit trails and approvals server-side. Opinion post with no benchmarks or code.

Model Context ProtocolDockerTerraform+5
Kizuno18HCP TerraformOPA

mcp· Added 29 Oct 2026, published 27 Oct 2026

x.comthread🛡️ Security

Buchi Reddy B (@buchireddy) on X

Buchi Reddy B's X thread comments on Forever Security's research (Gal Weizman, Omer Samet) on coding agents. A web page silently writes a fake AGENTS.md or CLAUDE.md into a Downloads folder, and Codex and Claude Code follow it as project rules. Codex then wrote an attacker's MCP server into the machine-wide config, so one injection becomes a standing connection for every session. It asks whether teams inventory runtime MCP connections against approved lists.

CodexClaude CodeModel Context Protocol
Forever SecurityGal WeizmanOmer Samet+3

AI Security· Added 28 Oct 2026, published 27 Oct 2026

x.comthread🧠 AI

Rohan Paul (@rohanpaul_ai) on X

Hi3D v1.0 (formerly Sparc3D) is an open-sourced image-to-3D model from Hi3D, which runs a closed v3.0 refining at 2048 cubes per side. In a test with 13 professionals in 3D algorithms, 562 judgments against eight other image-to-3D models favoured it 83.5% of the time. The thread also covers the Hi3D Agent and an MCP server for other agents. Back and bottom views were checked, where TRELLIS.2 collapsed a winged figure.

Model Context Protocol
Hi3DHi3D v1.0Sparc3D+2

models, multimodal, mcp· Added 28 Oct 2026, published 27 Oct 2026

x.comthread🛡️ Security

cubillas (@cubillas888) on X

The tweet relays Pillar Security research that opencode on Windows and WSL could run attacker-controlled code during remote MCP server OAuth sign-in. The fix shipped in opencode 1.18.33 on 28 September, with no advisory or CVE published. It advises users of remote MCP servers to update and review which servers they connect to. Technical details are not in the post.

OpenCodeModel Context ProtocolOAuth+1
Pillar Security

AI Security, AppSec· Added 29 Oct 2026, published 27 Oct 2026

x.comthread🛡️ Security

Nicholas Martin (@ndgmlondon) on X

X thread started by Nicholas Martin (#IAM) advising that MCP tool permissions be verified and scoped session tokens used to enforce least privilege against indirect prompt injection. Replies argue that token scoping does not solve the confused deputy problem, because an injection borrows the agent's legitimate authority. They recommend per-task tokens with short expiry, with the grant logged beside the call, and raise MCP server dependency supply-chain risk.

Model Context Protocol
indirect prompt injectionconfused deputy

AI Security, Identity & Access· Added 28 Oct 2026, published 27 Oct 2026

arxiv.orgpaper🛡️ Security

Measuring Users' Security and Privacy Concerns About Third-Party Community Bots on Discord

Measurement study of 23,102 third-party Discord bots and 183,142 user reviews (2021-2026, 49 languages). A fine-tuned DeBERTa classifier plus manual validation yields 8,832 security and privacy reviews, mapped to a 31-theme taxonomy; Data Sharing (30.5%) and Data Collection (16.2%) dominate. Permission count and admin status correlate only weakly with user concerns. The authors build BotLens, an MCP-server auditing framework with six tools.

DiscordModel Context ProtocolLLM
BotLensDeBERTa

other, AI Security· Added 28 Oct 2026, published 27 Oct 2026

arxiv.orgpaper🛡️ Security

Log-To-Leak: Prompt Injection Attacks on Tool-Using LLM Agents via the Model Context Protocol

Log-To-Leak is a prompt-injection attack on tool-using LLM agents that abuses Model Context Protocol tool metadata to trigger an attacker-controlled logging call after the last legitimate call, leaking the user query, server name, server response and agent response. Evaluated on five MCP servers and four agents, it reaches 62.64-100% attack success with 76.55-95.64% logging accuracy. Three defenses leave over 55% residual ASR on GitHub MCP with GPT-4o.

Model Context ProtocolGitHubGPT-4o+1
Log-To-Leaktool poisoningprompt injection

AI Security· Added 28 Oct 2026, published 26 Oct 2026

x.comthread🛡️ Security

David Gutierrez | Eng (@david_x_ai) on X

Thread on two October 2026 npm compromises: @subql/common 5.8.3 (5 October), published through GitHub Actions OIDC Trusted Publishing after the attacker tampered with the publish workflow, and tensorlake 0.5.144 (8 October), published by the project's own release workflow with valid provenance for about 1 hour 40 minutes. Both ran on install and stole cloud, GitHub, Kubernetes, Vault, SSH and .env credentials; tensorlake also took AI tool and MCP config. Its payload installed a gh-token-monitor service that deletes the home directory if the stolen GitHub token is revoked, so remove it before rotating.

npmGitHub ActionsGitHub+3
@subql/commontensorlakegh-token-monitor+3

Supply Chain, DevSecOps· Added 27 Oct 2026, published 26 Oct 2026

x.comthread🛡️ Security

Benjamin👨‍💻 (@Hislordship_9) on X

Thread on Forever Security's finding that a planted Markdown "Engineering Work Guidelines" file in ~/Downloads made Codex add a "project-tools" MCP server to ~/.codex/config.toml. The server ran npm install function-color, a known malicious package, and started a child session with --dangerously-bypass-approvals-and-sandbox. Codex complied in over 90% of the firm's tests; Claude Code, via a CLAUDE.md setting ANTHROPIC_BASE_URL, about half. Advice: don't start agents in Downloads, review instruction files, and diff agent config.

CodexClaude CodeModel Context Protocol+1
Forever Securityfunction-colorAGENTS.md+4

AI Security, Supply Chain· Added 27 Oct 2026, published 26 Oct 2026

x.comthread🛡️ Security

David Gutierrez | Eng (@david_x_ai) on X

Thread on a critical opencode bug disclosed by Pillar Security on Oct 19. On Windows and WSL, a remote MCP server could run code during OAuth sign-in, because the server-chosen authorization URL was put unescaped into a PowerShell command, so a PowerShell subexpression executed. opencode fixed it in 1.18.33 on Sep 28 as a browser-launch refactor with no advisory or CVE. MCP Inspector published an advisory for the same bug class, and its fix needs a major bump of the open package.

OpenCodeModel Context ProtocolPowerShell+3
Pillar Securitycommand injectionPowerShell subexpression+1

AI Security, AppSec, Supply Chain· Added 27 Oct 2026, published 25 Oct 2026

x.comtool🧠 AI

Dan Kornas (@DanKornas) on X

jshook is an open-source (AGPL-3.0) MCP server that gives AI agents a search-first, profile-aware reverse-engineering workspace for JavaScript, browser traffic, WASM and native processes. Agents start with a small searchable tool surface and move to workflow or full profiles only when needed. It drives Chromium or Camoufox over CDP, captures WebSocket traffic, has HTTP, GraphQL and Burp Suite helpers, and supports hot-reload plugins and declarative workflows. The post is a short announcement; the repository link is in a reply.

Model Context ProtocolJavaScriptWebAssembly+6
jshookDan Kornas

mcp, agents· Added 28 Oct 2026, published 25 Oct 2026

x.comtool🛡️ Security

Dan Kornas (@DanKornas) on X

jshook is an open-source (AGPL-3.0) search-first reverse-engineering workspace for AI agents, exposed over MCP. It drives Chromium or Camoufox through CDP, captures WebSocket traffic, offers HTTP, GraphQL and Burp Suite helpers, deobfuscates JavaScript, rebuilds source maps and disassembles WebAssembly. Tool profiles start small and expand to workflow or full sets; hot-reload plugins and declarative workflows extend it.

Model Context ProtocolBurp SuiteChrome+3
CamoufoxCDP

Malware & RE, AI Security, Offensive Security· Added 28 Oct 2026, published 25 Oct 2026

x.comtool🧠 AI

Agent Credit (@agentcredit_) on X

Agent Credit v1.3 is a remote MCP server that lets AI agents run credit checks on each other. It has six tools: score, compare, operator record, alerts and on-chain proof check. Calls are paid per use in USDC through x402 with no account or key. It also flags shared wallets, lists every token an operator launched and how each ended, and offers embeddable badges and wallet-signed record claims.

Model Context Protocolx402USDC+1
Agent Credit

mcp, agents· Added 26 Oct 2026, published 25 Oct 2026

mcpmarket.comtool🧠 AI

Search Search results for "security" | MCP Market

MCP Market search results for "security" in its skills category, listing about 20 installable AI agent skills. Entries cover OWASP Top 10 audits, secure PHP coding, STRIDE threat modeling, CVE remediation, security header analysis, misconfiguration finding, bug bounty triage and AgentShield scans of Claude Code configurations. One is a paid D365FO security-role XML skill. Each entry has only a one-line description and a category label.

Claude CodeAgentShieldPHP+1
MCP MarketOWASPSTRIDE

coding-agents, prompting· Added 25 Oct 2026

mcpmarket.comother🛡️ Security

Search Search results for "security" | MCP Market

MCP Market search results for "security" in the skills category, listing about 20 installable AI agent skills. Entries cover OWASP Top 10 audits, secure coding for PHP, STRIDE threat modeling, CVE remediation, security header analysis, misconfiguration finding, bug bounty triage and AgentShield scans of Claude Code configurations. One is a paid D365FO security-role XML skill. Each entry has only a one-line description and a category label.

Claude CodeModel Context ProtocolPHP
OWASPSTRIDEAgentShield+1

AppSec, AI Security· Added 25 Oct 2026

x.comthread🧠 AI

Big Bull (@BIGBULLapp) on X

5ire is a desktop AI assistant and MCP client that connects to OpenAI, Anthropic, Google, Mistral, Grok, DeepSeek and Ollama from one window. It has a local knowledge base and tool calls over Model Context Protocol. The tools feature needs Python, Node and uv installed because it runs a local MCP server; without them it works only as a chat client.

Model Context ProtocolPythonNode.js+3
5ireOpenAIAnthropic+4

mcp, llm-apps· Added 25 Oct 2026, published 24 Oct 2026

x.comthread🧠 AI

ReignSwords (@ReignSwords) on X

A reviewer tests GenOffice, an open-source Office suite (10.7k GitHub stars), through its CLI only. Markdown to .docx took 3.8s, JSON to .xlsx took 0.9s with a live SUM formula, and .docx to PDF failed twice until Xvfb supplied a display. It has byte-preserving edits, a skill file for Claude Code and Codex, and 29 MCP tools. Downsides: a 188MB download that filled a 512MB /tmp, Electron in the PDF path, and unproven trust in tracked changes and rollback.

Model Context ProtocolClaude CodeCodex+4
GenOffice

mcp, coding-agents, agents· Added 25 Oct 2026, published 24 Oct 2026

x.comthread🧠 AI

Gökdeniz Gülmez (@ActuallyIsaak) on X

An X post showing how to have Codex train a small model on Apple silicon through the mlx-lm-lora MCP server and skill. It gives five setup steps (pip install with the mcp extra, npx skills add, locate mlx-lm-lora-mcp, codex mcp add). The prompt runs four pre-training trials on tiny-random/qwen3 with the mlx-community/recycling_the_web-1k dataset. Codex picks the optimizer and learning rate itself, and the result is a table with validation loss and the best adapter path.

CodexMLXModel Context Protocol+5
mlx-lm-loraGoekdeniz-Guelmeztiny-random/qwen3+2

training, mcp, coding-agents· Added 25 Oct 2026, published 24 Oct 2026

x.comthread🧠 AI

Prasenjit Sarkar (@stretchcloud) on X

Post explaining Claude's new support for MCP Tasks and Elicitations. A server returns a durable task handle instead of blocking. The client polls tasks/get every 250 ms to 30 s, and states are working, input_required, completed, failed or cancelled. Elicitations pause a task at input_required for human approval. It also notes Cloudflare's stateless MCP servers and Code Mode, and Sentry and Linear adoption.

Model Context ProtocolClaude CodeGitHub Actions+3
AnthropicClaudeAWS+4

mcp, agents· Added 25 Oct 2026, published 24 Oct 2026

x.comthread🧠 AI

EveryDev.ai (@EveryDevAi) on X

ToolUniverse, from ScientistTools, is an open-source (Apache-2.0) toolkit that gives any LLM one interface to more than 1,000 scientific tools, models and databases such as PubMed, UniProt and ChEMBL. It ships a native MCP server, a Python SDK and a tu CLI, plus 68 pre-built agent skills. The post says it works with Claude Code, Cursor, Gemini CLI and Windsurf.

Model Context ProtocolPythonClaude Code+4
ToolUniverseScientistToolsPubMed+2

mcp, agents· Published and added 24 Oct 2026

arxiv.orgpaper🛡️ Security

Deletion, Substitution, Repair and Transplant: Component Attribution in BARBICAN, a Layered Prompt-Injection Gateway for MCP

BARBICAN is a fail-closed prompt-injection gateway for MCP tool mediation. This paper shows its arbitration classifier ran on tokenizer-mangled text for a whole evaluation. Fixing it raised AUC from 0.392 to 0.855 while system recall fell from 80.67% to 80.34%. The routed band is 96.82% malicious, so deletion ablations mislead without substitution experiments and class-balance reporting.

Model Context ProtocolLLM
BARBICANprompt injection

AI Security· Added 27 Oct 2026, published 23 Oct 2026

arxiv.orgpaper🧠 AI

Deletion, Substitution, Repair and Transplant: Component Attribution in BARBICAN, a Layered Prompt-Injection Gateway for MCP

The paper analyses BARBICAN, a fail-closed prompt-injection gateway for MCP tool mediation, using deletion, substitution, repair and transplant experiments. Its arbitration classifier ran on tokenizer-mangled text for a whole evaluation. Fixing that raised AUC from 0.392 to 0.855 while system recall fell from 80.67% to 80.34%. The band it receives is 96.82% malicious. The authors argue ablation figures need the band's class balance and substitution baselines.

Model Context Protocol
BARBICAN

evals, research, mcp· Added 27 Oct 2026, published 23 Oct 2026

endorlabs.comarticle🛡️ Security

ADLC Security Best Practices for Teams Shipping with Coding Agents | Endor Labs

ADLC Security Best Practices is an Endor Labs guide to controlling what AI coding agents can access, run, install and ship. It covers inventorying agents and MCP servers, sandboxing, pre-execution hooks instead of AGENTS.md rules, install-time package checks against slopsquatting and malware, reachability-based triage of agent PRs, and CI/CODEOWNERS protections. A five-step worked example and coverage metrics are included.

Model Context ProtocolClaude CodeCursor+3
slopsquattingindirect prompt injectiontool poisoning+5

AI Security, Supply Chain, DevSecOps· Published and added 23 Oct 2026

x.comthread🧠 AI

Yash Patil (@yvshpvtil) on X

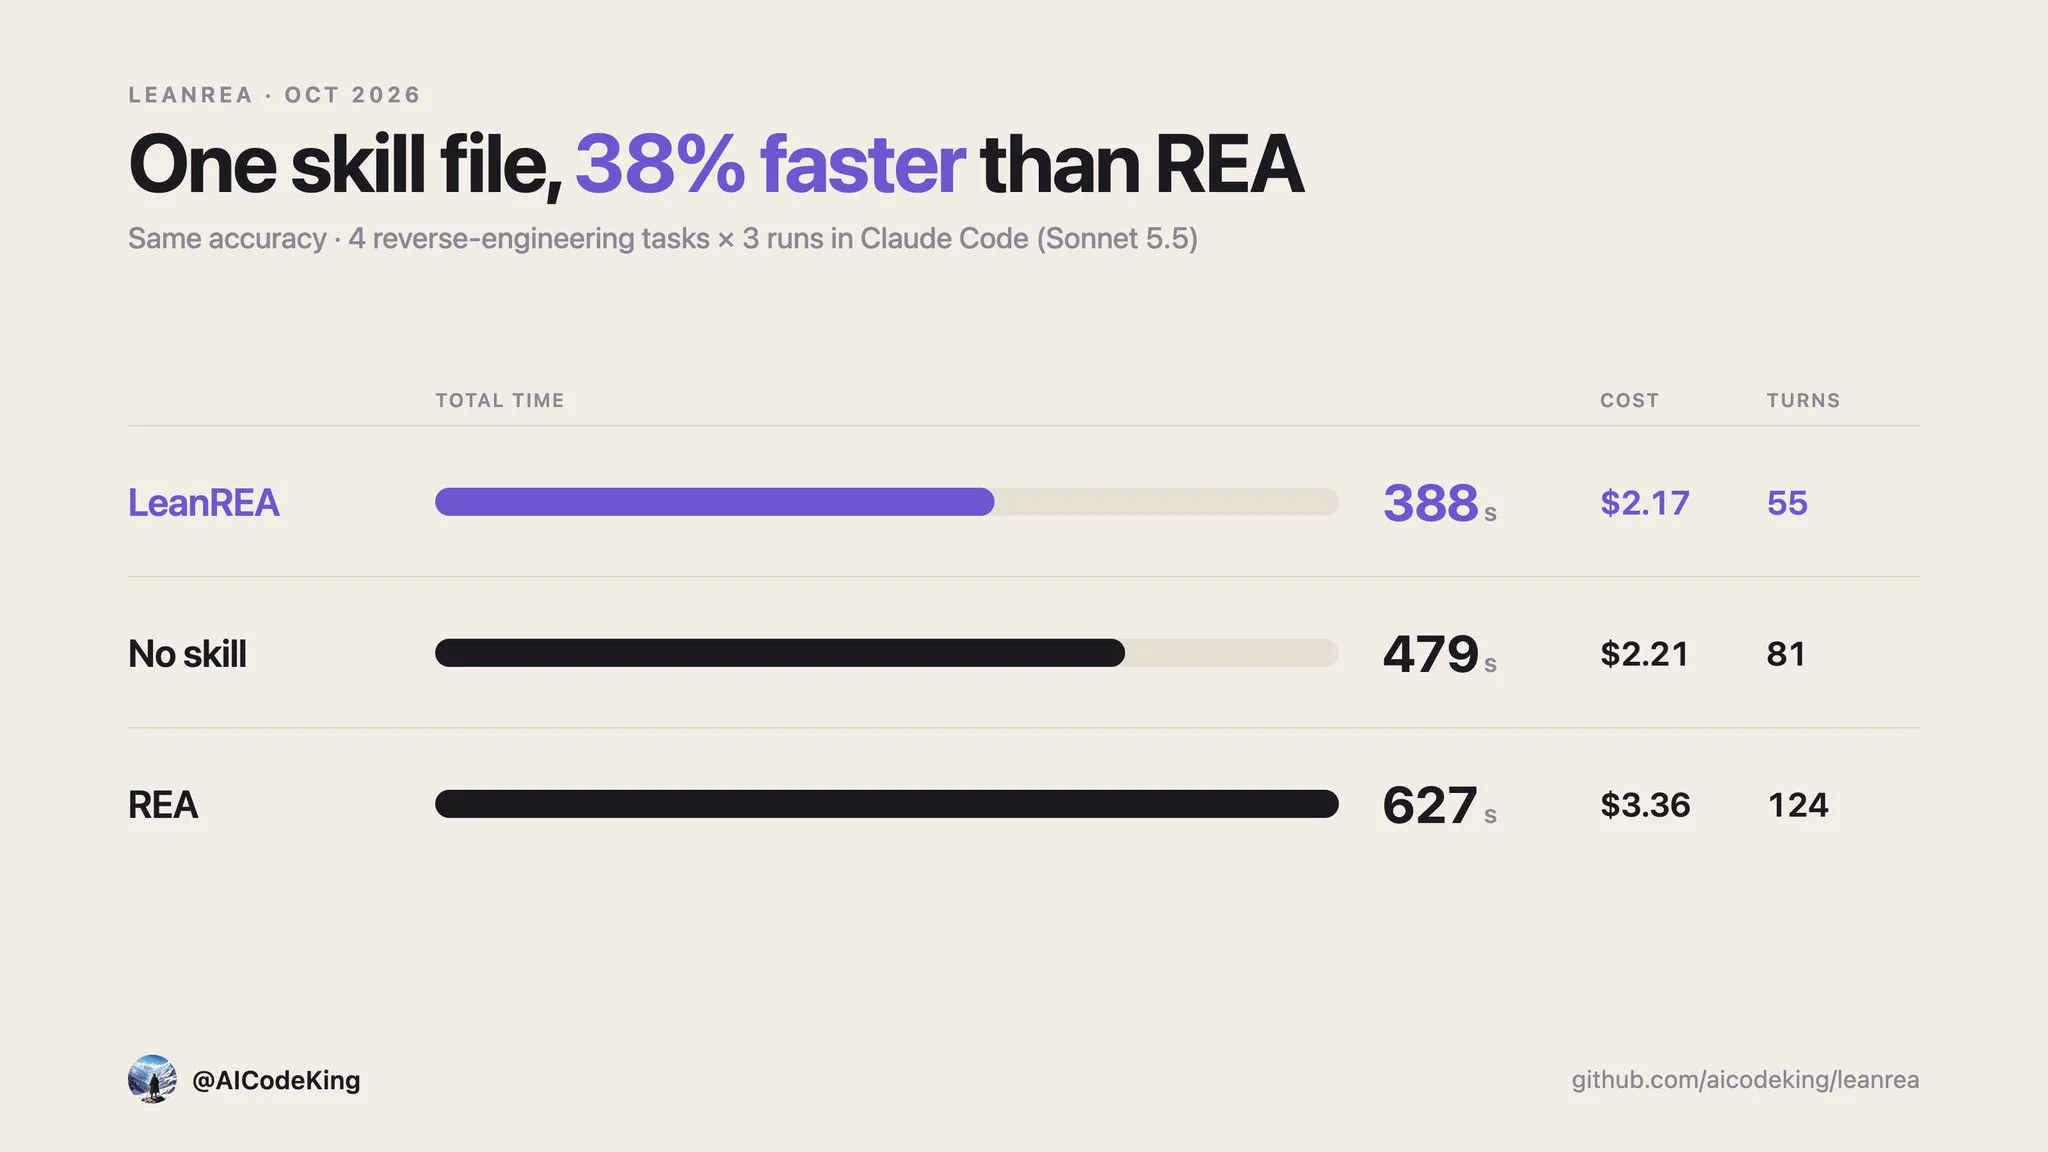
leanrea is an 8 KB skill file that tells a coding agent which plain CLI tools to use for reverse engineering, replacing REA, a 207-tool MCP server. In the author's test it ran 38% faster and 35% cheaper, scoring 74/75 against 75/75. The author lists caveats: 3 runs per task, one model, one machine, and Claude with no skill was already decent.

Model Context ProtocolClaude
leanreaREAYash Patil+2

prompting, mcp, coding-agents· Added 25 Oct 2026, published 23 Oct 2026

x.comthread🛡️ Security

Yash Patil (@yvshpvtil) on X

leanrea is an 8 KB skill file that tells a coding agent which plain CLI tools to use for reverse engineering, replacing the 207-tool REA MCP server. The author's test reports 38% faster, 35% cheaper, and a score of 74/75 against REA's 75/75. Caveats listed: 3 runs per task, one model, one machine, and Claude with no skill already performed decently. Replies question whether the lost point was a task where structured tool output beat parsing CLI text.

leanreaREAModel Context Protocol+1

Malware & RE, AI Security· Added 25 Oct 2026, published 23 Oct 2026

arxiv.orgpaper🧠 AI

Tool-Calling LLM Agents Under Realistic MCP Faults: Scale Does Not Purchase Fault Tolerance

MCP-Injector is a protocol-aware fault-injection middleware for Model Context Protocol tool calls, with permanent, transient and intermittent faults on seedable schedules. Its fault model comes from 57,240 issue and PR threads across 1,774 open-source MCP repositories. In a 1,350-cell experiment, faults cut task-completion score by 60% (8.08 to 3.23 of 10), and the 120B gpt-oss model was no more resilient than the 20B. Agent stacks differed in how well they absorbed faults.

Model Context ProtocolOpenAI Agents SDKLangChain+2
MCP-Injectorgpt-oss-120bOpenAI

mcp, evals, agents, research· Added 26 Oct 2026, published 23 Oct 2026

arxiv.orgpaper🛡️ Security

Agentic AI Defense: Decode-Time Provenance Binding for MCP

Decode-time provenance binding is a defense for Model Context Protocol agent pipelines against cross-modal trust laundering, where instructions hidden in an email-signature image via LSB, DCT or metadata steganography get decoded by a tool. It combines HMAC-authenticated trust labels, a provenance ledger and context-taint tracking to block critical tool calls. On a real MCP testbed with 24 adaptive payloads, attack success fell from 100% undefended (62.5% for keyword and regex filters) to 0%.

Model Context Protocol
indirect prompt injectioncross-modal trust launderingsteganography+5

AI Security· Added 26 Oct 2026, published 22 Oct 2026

simonwillison.netarticle🧠 AI

Donating Agent Skills to the Agentic AI Foundation

Simon Willison's link post covers Anthropic's 22 October 2026 announcement that it is donating the Agent Skills standard to the Agentic AI Foundation (AAIF) under the Linux Foundation. Anthropic co-founded the AAIF with Block and OpenAI and earlier donated MCP to it. Willison notes he predicted this in December 2025 and found his old post by querying his blog through datasette-mcp in Claude.

Model Context ProtocolClaudeDatasette
AnthropicAgentic AI FoundationLinux Foundation+3

prompting, ai-policy, coding-agents· Published and added 22 Oct 2026

x.comtool🧠 AI

Meku_SI (@MEKU_SI) on X

MEKU Human Cloud is an MCP server for agents that need a real person to do a task. It exposes three tools: search humans (read-only), request a human (a human operator reviews every request first), and check status. It is listed in the MCP Registry as farm.meku/human-cloud. The tweet gives no detail on pricing, humans available or request formats; those are in the linked docs.

Model Context Protocol
MEKU Human CloudMeku_SI

mcp, agents· Added 23 Oct 2026, published 22 Oct 2026

x.comrepo🧠 AI

Dan Kornas (@DanKornas) on X

aula-mcp is an open-source (MIT) TypeScript MCP server that connects an AI client to Denmark's Aula school platform. It exposes tools for profiles, calendar events, messages, notifications, posts and weekly plans. MitID credentials and OAuth tokens are stored in macOS Keychain or an AES-256-GCM encrypted file. The HTTP server binds to 127.0.0.1, and the presence write tool stays off until AULA_MCP_WRITE=1 is set.

Model Context ProtocolTypeScriptClaude Code+3
AulaMitIDDan Kornas

mcp· Added 23 Oct 2026, published 22 Oct 2026

x.comthread🧠 AI

SpyTech Ai (@RizeOnline) on X

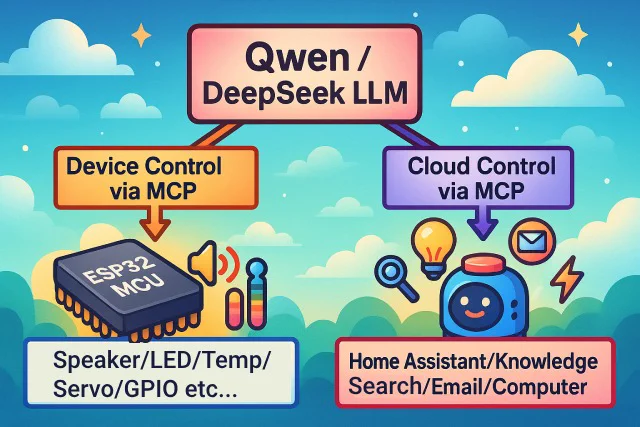
XiaoZhi ESP32 is an open-source, MIT-licensed firmware stack that turns ESP32 boards into MCP-based voice chatbots using models such as Qwen and DeepSeek. It streams Opus audio over WebSocket or MQTT + UDP through ASR, LLM and TTS, adds offline ESP-SR wake words, and uses device-side MCP to drive speakers, LEDs, servos and GPIO. It supports 138 board directories and builds with ESP-IDF 6.0.1 or newer.

Model Context ProtocolESP32ESP-IDF+10
XiaoZhi ESP32SpyTech Ai

mcp, multimodal, llm-apps· Added 23 Oct 2026, published 21 Oct 2026

x.comthread🛡️ Security

VibecodersHQ (@VibeCodrHQ) on X

Post summarising Pillar Security's finding of a remote code execution flaw in OpenCode, the open-source AI coding agent. Versions 1.0.137 through 1.18.32 could run code from a remote MCP server during OAuth sign-in on Windows and WSL, with no prompt injection needed. The fix is in 1.18.33 (released 28 September). No advisory or CVE was issued, so scanners will not flag old installs. Interim advice is to remove unvetted remote MCP servers.

OpenCodeModel Context ProtocolOAuth+1
Pillar SecurityOpenCode Console breach

AI Security, AppSec· Added 22 Oct 2026, published 21 Oct 2026

x.comthread🛡️ Security

Swif (@swif_ai) on X

Swif (@swif_ai) reports that in the MCP TypeScript server SDK versions 2.0 to 2.2, a single server instance shared by several HTTP clients, which is the pattern the README shows, could send one client's responses to another client. Version 2.3.0 refuses this setup, so developers must build a server per request or per session. The post gives no CVE, advisory ID or technical detail.

Model Context ProtocolTypeScript
cross-client data leak

AI Security, AppSec· Added 22 Oct 2026, published 21 Oct 2026

x.comthread🧠 AI

Swif (@swif_ai) on X

A post from Swif (@swif_ai) on the MCP TypeScript server SDK versions 2.0 to 2.2. A single server instance shared across HTTP clients, the pattern shown in the README, could send one client's responses to another client. Version 2.3.0 refuses that setup, so servers must be built per request or per session. The post gives no code or advisory ID.

Model Context ProtocolTypeScript
Swif

mcp· Added 22 Oct 2026, published 21 Oct 2026

github.comrepo🧠 AI

Show HN: Omnara – Open-source alternative to Claude Managed Agents

Omnara is an open-source, self-hostable managed agent platform, an alternative to Claude Managed Agents and OpenAI's Agents API. It runs agents on any model (OpenAI, Anthropic, OpenRouter, Bedrock, LiteLLM, Ollama) and any machine, with Postgres-backed durable state, stateless workers, per-tool permissions, MCP, skills, memory, subagents, schedules and Slack, Discord and GitHub triggers. It ships a REST API, TypeScript SDK, CLI and Docker Compose setup.

Model Context ProtocolTypeScriptNode.js+14
OmnaraClaude Managed AgentsOpenAI+2

agents, ai-infra, mcp· Added 23 Oct 2026, published 21 Oct 2026

aikido.devarticle🛡️ Security

Software supply chain security best practices for 2026

Aikido's guide to software supply chain security controls for 2026, tied to real incidents. It covers a 48-hour package cooldown, ignore-scripts, lockfile enforcement, SHA and digest pinning, scoped tokens, FIDO2, developer endpoint protection, extension allowlists, agent sandboxing, MCP server vetting, slopsquatting, signed SBOMs and rotation drills. Examples include the March 2026 axios compromise and the March 2025 tj-actions/changed-files attack.

npmpnpmGitHub Actions+3
tj-actions/changed-filesCanisterWormGlassWorm+7

Supply Chain, DevSecOps, AI Security· Added 22 Oct 2026, published 21 Oct 2026

blog.cloudflare.comarticle🧠 AI

How Commerce.com and Cloudflare are getting storefronts ready for AI agents

Cloudflare and Commerce.com describe enabling WebMCP, Google's proposed browser standard for exposing structured tools to AI agents, across almost 100,000 storefronts. Cloudflare injects a bridge script at the edge that proxies tools from Commerce.com's backend MCP server. Per-merchant opt-out uses Configuration Rules and custom hostname metadata, and a configurable MCP URL (/api/mcp) was added.

WebMCPModel Context ProtocolCloudflare+3
Commerce.comGoogleKristina Pototska+1

mcp, agents· Added 29 Oct 2026, published 21 Oct 2026

alterauth.comtool🧠 AI

Launch HN: Alter (YC S25) – Access control for multi-user agents

Alter is a privileged access management layer for AI agents (YC S25). It stores credentials in a vault, injects them per request through a proxy, gives each agent its own identity and scoped grants, and logs every call to a tamper-evident audit trail. One SDK call covers storage, refresh, policy and audit for 140 API providers, with LangChain, MCP and AWS integrations. Policy is default-deny down to the parameter, with human approval for risky calls.

Model Context ProtocolLangChainAWS+3
AlterY Combinator

ai-infra, agents· Added 22 Oct 2026, published 21 Oct 2026

snyk.ioarticle🛡️ Security

AI Model Risk Depends on What the Model Can Reach

Snyk's State of Agentic AI Adoption Volume III scores models against 29 attacker goals (0 to 1,000) and matches them to AI-BOM scan data from 1,693 environments. 74.5% reference a model scoring 500+ on some goal and 49.2% one scoring 750+. Risk depends on agent and MCP server reach, and the fix is either switching models or tightening application controls, depending on the goal. Only 37.5% of model occurrences have a score.

SnykModel Context ProtocolLLM
State of Agentic AI Adoption Volume IIIAI-BOMEpoch Capabilities Index+2

AI Security, GRC· Published and added 21 Oct 2026

arxiv.orgpaper🛡️ Security

Combining Long-Term Memory and LLMs Comes at a High Cost: From Prompt Injection to Persistent Compromise

Paper on memory injection, where prompt injection persists across sessions through the long-term memory of LLM-as-a-service platforms. It presents a general threat model and shows all NIST attack goals are achievable on ChatGPT Instant 5.3, Claude Sonnet 4.6 and Gemini 3 Flash. Vectors include personal memories, projects, skills, organization instructions and MCP resources. On Claude, shared memory lets an attacker compromise multiple users in an organization and exfiltrate prompts. Nearly half of the derived mitigations are unimplemented.

ChatGPTClaudeGemini+2
memory injectionprompt injectionNIST+2

AI Security· Added 24 Oct 2026, published 20 Oct 2026

x.comthread🧠 AI

Paulo Pierrondi | AI agents (@paulopierrondi) on X

Paulo Pierrondi's X post, part 9 of a series on installing MCP servers, lists a monthly review of installed servers. The checks are which tools the agent used, servers not called in weeks, overlapping tools that confuse the model, and whether each server still has an owner. A reply adds a decommissioning check: after removal, confirm the server's old credentials can no longer call the backend.

Model Context Protocol
Paulo Pierrondi

mcp· Published and added 20 Oct 2026

x.comthread🛡️ Security

DFIR Radar (@DFIR_Radar) on X

DFIR_Radar weekly detection engineering digest covering 23 new and 19 updated rules across 6 GitHub repositories. It lists KQL rules for Azure Key Vault secret retrieval, MCP client User-Agent bulk operations and local Azure token theft, AWS CloudTrail analytics, Sigma rules for firewall and ETW tampering (decimal 17 vs hex 0x11), updated LOLDrivers hashes, and Sublime email rules for OAuth consent phishing and fake IRS W-9 PDFs.

KQLSigmaMicrosoft Sentinel+3
BYOVDCisco AI Defensebenscha/KQLAdvancedHunting+7

Blue Team & Detection, Cloud & Infra, AI Security· Added 20 Oct 2026, published 19 Oct 2026

x.comarticle🛡️ Security

Huda (@AlAssaf_H) on X

Source-level review of x64dbg-MCP, GhidraMCP and IDA Pro MCP security, dated October 2026. It covers GHSA-4478-h5jv-647m (missing authentication, 0.0.0.0 bind) and GHSA-jgj3-97w2-9v9r (Content-Length integer overflow before the token check, causing a DoS panic), and compares tags 1.0, v1.1 and v1.2. It separates network reachability, tool authority and semantic influence from hostile binaries. No new exploit is claimed.

Model Context ProtocolGhidrax64dbg+2
GHSA-4478-h5jv-647mGHSA-jgj3-97w2-9v9rprompt injection+5

AI Security, Malware & RE· Added 21 Oct 2026, published 19 Oct 2026

x.comrepo🛡️ Security

Panos Gkatziroulis 🦄 (@ipurple) on X

Malvex (JoasASantos/Malvex) is an AI-driven malware analysis framework that integrates more than 30 analysis tools, a web REPL and an MCP server. Panos Gkatziroulis shared it on 19 October 2026 and noted that it was written by AI. The tweet gives no detail on which tools are bundled or how the AI drives them.

Model Context ProtocolGitHubLLM
Malvex

Malware & RE, AI Security· Added 22 Oct 2026, published 19 Oct 2026

x.comthread🧠 AI

Angel (@ziran_pu) on X

AshAi, the AI package for the Elixir Ash Framework, is getting MCP client tools. Creating an MCP server with AshAi was already simple, but connecting your own LLM tool loop to an external MCP server had to be built by hand. The planned release includes OAuth client management resources. The post gives no release date, API details or code.

Model Context ProtocolAsh FrameworkAshAi+2

mcp· Added 21 Oct 2026, published 19 Oct 2026

x.comthread🛡️ Security

Santhosh Patel (@santhosh_patell) on X

Summary of Pillar Security research on opencode, in which a malicious remote MCP server runs code on a Windows or WSL machine during the OAuth login step. The login URL goes unsanitised into PowerShell through the npm "open" package, so an https:// link containing $(...) executes. Affected versions are 1.0.137 to 1.18.32, fixed in 1.18.33 (28 September) as a "refactor" with no advisory or CVE. The behaviour was first reported in 2020 as a WSL 2 broken-link bug.

OpenCodeModel Context ProtocolPowerShell+3
Pillar SecurityCWE-78silent fix

AI Security, AppSec, Supply Chain· Added 21 Oct 2026, published 19 Oct 2026

x.comrepo🧠 AI

Saylor (@Kev96790724) on X

G-Krusch is an MIT-licensed, local-first Google Workspace hub built on Node.js 22 and SQLite WAL. It runs a 12-tool MCP server (SSE and Stdio) plus a REST bridge on port 5446 for Drive, Calendar and Gmail. It includes a 1,024-dimension hybrid Drive RAG with an embedding cascade (Ollama bge-large, then Gemini, then offline fallback) and FTS5 BM25. PDF extraction returns page citations. Tokens are kept in an AES-256-GCM vault; 30 of 30 tests pass.

Model Context ProtocolNode.jsSQLite+5
G-KruschKrusch CompanionKruschNexus+1

mcp, llm-apps, coding-agents· Added 21 Oct 2026, published 19 Oct 2026

github.comrepo🧠 AI

Show HN: WhatsApp MCP running free on Cloudflare

whatsapp-mcp is an MCP server that runs in the user's own Cloudflare account and lets MCP clients such as Claude Code and Claude Desktop search and read WhatsApp chats. It links as a WhatsApp Web-style device through Baileys, stores messages in SQLite with FTS5 inside a Durable Object, and is read-only. The README documents deployment, OAuth sign-in, contact naming through agents, and workerd shims for Baileys.

Model Context ProtocolCloudflareCloudflare Workers+11
WhatsApp

mcp· Added 20 Oct 2026, published 18 Oct 2026

x.comthread🛡️ Security

FastFix AI (@FastfixAI) on X

FastFix AI thread giving six checks before installing a plugin, MCP server or skill for a coding agent. It starts from a 300K-star repo that an agent found writing to Claude Code, Codex and Copilot configs on install. Checks: read before running, inspect npm install scripts, verify the real repo against lookalike trojaned copies, pin versions, diff agent configs, and limit tokens and permissions.

Model Context ProtocolClaude Codenpm+2
--dangerously-skip-permissionspostinstalllookalike repository

AI Security, Supply Chain· Added 19 Oct 2026, published 18 Oct 2026

x.comtool🧠 AI

Dan Kornas (@DanKornas) on X

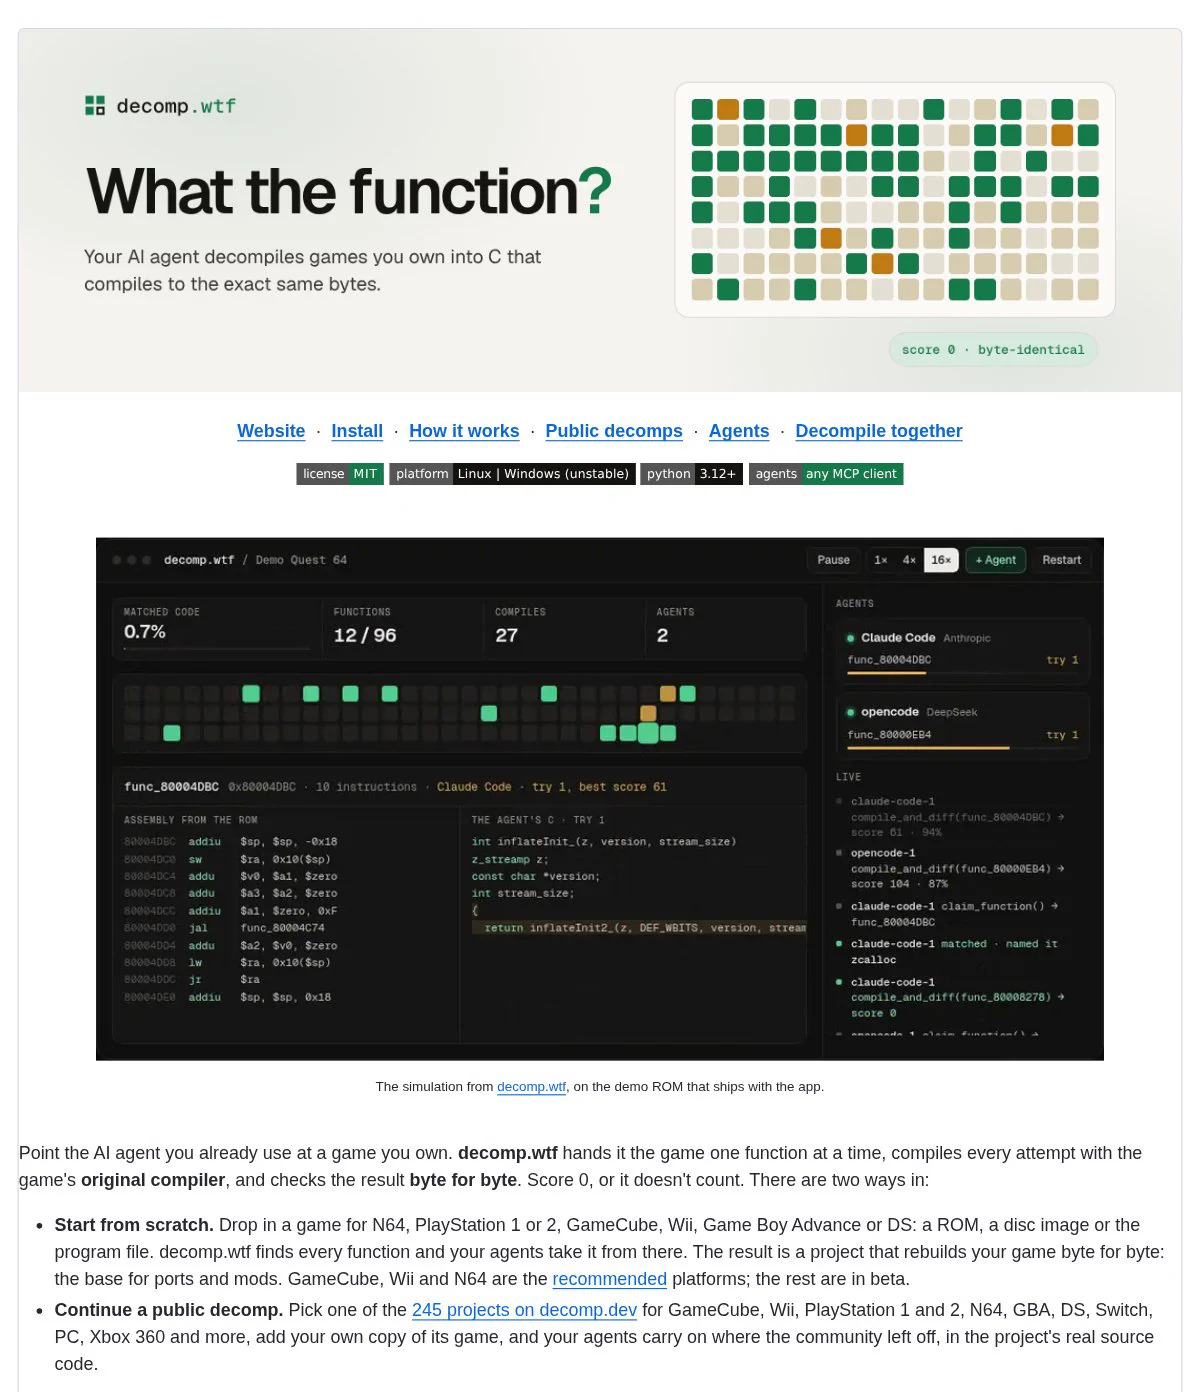
decomp.wtf is an open-source (MIT) local workspace where AI coding agents decompile games into C, one function at a time. Agents receive assembly, data, callers and earlier attempt notes, then each C candidate is compiled with the game's original compiler, linked at its real address and compared byte for byte, with instruction diffs on misses. It exposes MCP tools for Claude Code, Codex, Antigravity CLI and opencode, plus a live view of agent calls and match scores.

Model Context ProtocolClaude CodeCodex+3
decomp.wtfDan Kornas

coding-agents, mcp, agents· Added 19 Oct 2026, published 18 Oct 2026

x.comthread🛡️ Security

Magai (@HeyMagai) on X

Post from Magai (@HeyMagai) on Invariant Labs research showing that an approved MCP server can change its tool descriptions later without a new approval prompt, a "rug pull" like those in malicious code packages. It recommends pinning approval to tool definitions by hashing descriptions and re-prompting when the hash changes. For tools that move money, limits should stay server-side.

Model Context Protocol
Invariant LabsMCP rug pull

AI Security, Supply Chain· Added 19 Oct 2026, published 18 Oct 2026

arxiv.orgpaper🧠 AI

ToFu: Exploiting and Fuzzing the LLM–Orchestrator–Tool Trust Boundary

ToFu is a tool-aware fuzzing framework for LLM tools, including MCP servers. It maps each tool argument, using its metadata, to one of 74 CWE-guided semantics-aware sanitizers (path, URL, SQL and similar). It then generates schema-valid Atheris harnesses and semantic oracles, using runtime tracers for in-process tools and outcome oracles for opaque ones. The LLM (gpt-4.1) only maps sanitizers and writes seeds; it is never the security judge. The paper also shows a "Repeat-After-Me" trick, where an LLM told to repeat attacker-crafted text emits a tool call the orchestrator executes, reproduced on LangGraph, MAF, ADK 2.0, AutoGen, Strands and CrewAI. Across 273 runnable MCP servers (3,405 tools) it reports 253 verified bugs in 343 tools across 118 servers, such as path traversal, log injection and exfiltration. These are failures a crash-based fuzzer would miss. The result matters because it shows LLM-generated tool arguments cannot be treated as trusted.

Model Context ProtocolAtherisCodeQL+7
ToFuStrandsMAF+10

mcp, research, agents· Added 18 Oct 2026

arxiv.orgpaper🛡️ Security

ToFu: Exploiting and Fuzzing the LLM–Orchestrator–Tool Trust Boundary

ToFu is a tool-aware fuzzing framework that derives semantic security checks for LLM tools (mainly MCP servers) from their metadata and a corpus of 74 CWE-guided sanitizers. It generates schema-valid Atheris harnesses, uses runtime tracers and outcome oracles to catch bugs that don't crash, and uses an LLM only to map sanitizers and seed inputs, never as the judge. It also describes a "Repeat-After-Me" attack, in which the LLM is told to repeat attacker-written text that the orchestrator then dispatches as a tool call. It was reproduced on LangGraph, MAF, ADK, AutoGen, Strands and CrewAI. On 273 MCP servers it reports 253 verified bugs across 343 tools in 118 repositories, including path traversal, log injection, exfiltration and command bypass.

Model Context ProtocolAtherisLangGraph+3
Repeat-After-Mepath traversalSSRF+6

AI Security, AppSec· Added 18 Oct 2026

github.comrepo🧠 AI

eliasbiondo/antirion

Antirion is an open-source AI gateway shipped as one Rust binary with a built-in admin console. It sits between apps and providers such as OpenAI, Anthropic, Bedrock, Vertex and vLLM, translating between OpenAI, Anthropic, Gemini and Bedrock dialects. It covers routing with fallbacks and circuit breakers, budgets, guardrails, caching, MCP and A2A gateways, SSO, and a benchmark against Bifrost 2.2.4 and LiteLLM 1.103.1.

RustDockerKubernetes+13
AntirionBifrostOpenAI+10

ai-infra· Added 21 Oct 2026, published 17 Oct 2026

github.comrepo🧠 AI

ralphtradesz/trading-hub

Trading Hub is a free macOS desktop trading platform built with C#/.NET 10 and Avalonia. It uses the user's Claude Code subscription: a chat writes and fixes C# strategies, an in-app MCP server lets Claude run backtests, optimizations and walk-forwards and write reports, and a risk agent proposes position sizes. Install and a Windows port are both driven by Claude Code prompts. License is MIT with Commons Clause.

Claude CodeModel Context Protocol.NET+6
ClaudeATASDatabento+11

mcp, coding-agents· Added 19 Oct 2026, published 17 Oct 2026

x.comthread🛡️ Security

Steven Daugherty (@StevenDaugherty) on X

Post warning that FastMCP had a critical flaw where a malicious MCP server could execute code on the connecting client through a crafted tool schema. Fixed in FastMCP 3.4.8 and 4.0.11, and there is no patch for the 2.x line. It matters to anyone whose agents connect to MCP servers they don't control. The post gives no CVE ID or technical root cause.

FastMCPModel Context ProtocolPython
malicious MCP servercrafted tool schemaclient-side RCE

AI Security, AppSec· Added 18 Oct 2026, published 17 Oct 2026

github.comrepo🛡️ Security

OWASP/MCP-Security-Testing-Guide

OWASP MCP Security Testing Guide is a living, GPL-3.0 collection treating the Model Context Protocol as a security boundary from user through model, MCP client, MCP server and tool to the target system. It covers threats, secure development, host/client controls, supply chain, enterprise gateways, detection, incident response, taxonomy, public incidents, case studies and review checklists, with 79 tests in Chapter 3 (sections 3.1–3.19). It includes a finding template, and it links the MCP Goat lab for safe practice. It is useful to AppSec, red team and SOC people assessing MCP deployments.

Model Context ProtocolLLM
OWASPMCP Goat

AI Security, AppSec· Added 17 Oct 2026

github.comrepo🧠 AI

alex09x/kyb

KYB (Know Your Business) is a Rust/axum server that stores agent-written knowledge, incident reports and tasks as Markdown files in Git, one commit per change. Search is hybrid: Tantivy BM25 fused by reciprocal rank with local multilingual-e5-small ONNX vectors, and it can query historical versions or "as of" a date. It ships a kyb CLI, a native MCP endpoint (Claude Code, Codex, Antigravity, Gemini CLI), an installable agent skill, token auth with per-write attribution trailers, secret scanning on writes, and a web console. It targets persistent shared operational memory for multi-agent, multi-machine fleets.

RustGitModel Context Protocol+10
KYBAlexander Panasenkomultilingual-e5-small

agents, mcp, coding-agents· Added 17 Oct 2026

decrypt.coarticle🧠 AI

TokenMaxxing: How to Get the Most Out of Your AI Models

Decrypt guide to "tokenmaxxing" reframed as maximizing value per token rather than burning tokens. It gives tiered tips: pick smaller models for simple jobs, write one clear prompt, start new chats, cap output length, and use free models (beginner); Claude Code commands like /model, /clear, /compact, /context, /mcp, /effort and plan mode (intermediate); and prompt caching via cache_control, 50% batch discounts, and agent budget limits like --max-budget-usd (advanced). Includes context on Meta, Amazon and Uber token leaderboards and spend, a worked invoice-processing example where routing cut cost from $30 to $3.90, and the Jevons paradox in falling token prices.

Claude CodeClaudeChatGPT+8
DecryptAnthropicOpenAI+14

ai-infra, coding-agents, ai-policy· Published and added 17 Oct 2026

thingstodoapi.comtool🧠 AI

Show HN: Things to Do API

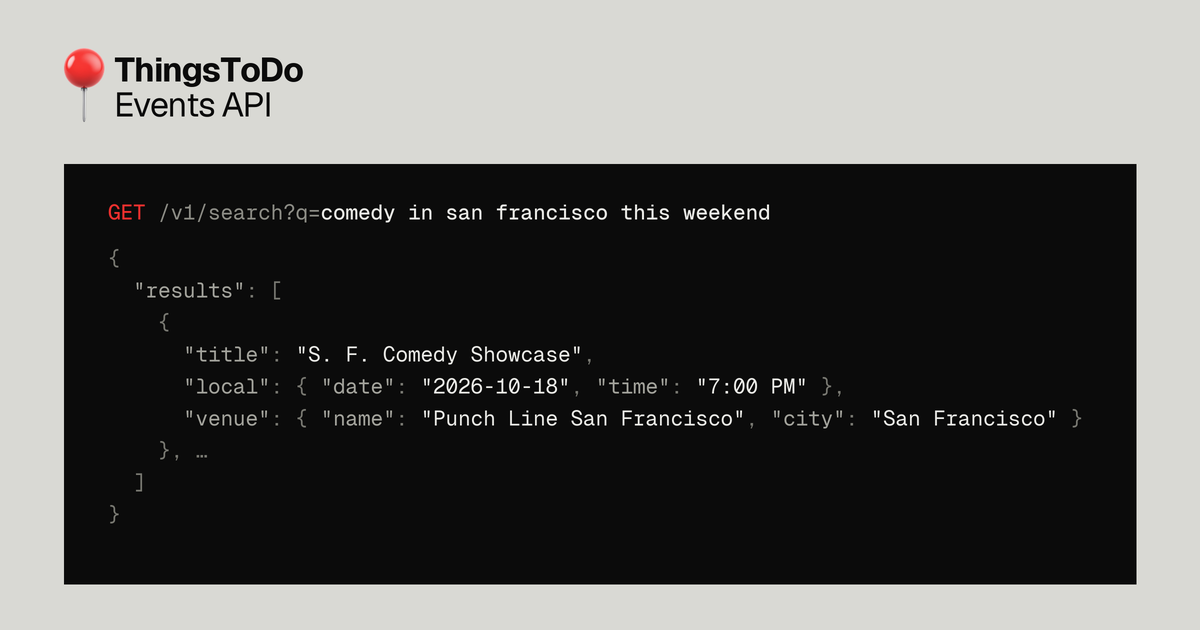
Things to Do API is a hosted knowledge base of local events (shows, talks, pop-ups, markets, festivals) that you query in natural language, for example `/v1/search?q=comedy+in+san+francisco+this+weekend`. It returns structured JSON with title, category, local start time, venue and ticket and source links. It also exposes an HTTP MCP endpoint, added with `claude mcp add --transport http thingstodo https://api.thingstodoapi.com/mcp`, so agents can use it as a tool. Coverage is live for the San Francisco Bay Area, with New York City and Los Angeles coming. Pricing is pay-as-you-go from $5 per 1,000 calls, the first 1,000 a month are free, and there is a 300 calls/min limit.

Model Context ProtocolClaude CodeREST
Things to Do APITicketmaster

mcp, llm-apps· Added 18 Oct 2026, published 16 Oct 2026

x.comthread🛡️ Security

Nicholas Martin (@ndgmlondon) on X

An X post advises auditing every MCP write tool against the database role it actually runs under. A shared service key lets prompt injection trigger unapproved writes, so each agent session should get a read-only role, with a test that writes are denied. Replies note that MCP servers often inherit ambient host credentials or can escalate through a second connection pool, and suggest also testing that another tenant's rows are unreadable with the same role.

Model Context Protocol
prompt injection

AI Security, Identity & Access· Added 18 Oct 2026, published 16 Oct 2026

securityweek.comarticle🛡️ Security

In Other News: ICS-Sniper Attack, Hacking XWorm Malware Operators, $250k Chrome Exploit

SecurityWeek's weekly roundup covers ICS-Sniper, a UBC proof-of-concept that uses VPN-encrypted packet size, direction and timing to drop critical SCADA traffic on cloud-hosted ICS (tested on the SWaT water testbed). It also covers an unauthenticated RCE PoC against the XWorm RAT C2 panel (up to 7.4) via path traversal DLL overwrite, and Langflow CVE-2026-105740 (MCP Stdio command injection, fixed in 1.9.0) exploited from September 19, before the CVE was published. Other items: XBOW's AI-assisted Chrome full-chain exploit (GPT-5.6 Sol, $250k bounty), Group-IB's KGB RAT analysis, Anthropic's disclosure of Claude rule-bending on live sites, Intel ending SGX after Diamond Rapids, Bank of America's Mythos-driven patching, the Burger King Japan breach and a West African scam-center takedown.

LangflowChromeXBOW+3
CVE-2026-105740ICS-SniperXWorm+12

Threat Intel, AI Security, Offensive Security· Published and added 16 Oct 2026

x.comthread🧠 AI

AmingIn_AI (@aming_inAI) on X

A tweet from AmingIn_AI describes a macOS screenshot-annotation tool. On release it saves the screenshot, a crop and the user's marks locally, then copies a 127.0.0.1 link. Claude Code or Codex on the same Mac can fetch that link and receive the marked image plus app/window info, and nothing is uploaded. It shows a local, privacy-preserving way to hand visual context to coding agents without MCP or cloud upload.

Claude CodeCodexmacOS
AmingIn_AI

coding-agents, multimodal· Added 17 Oct 2026, published 16 Oct 2026

x.comthread🛡️ Security

P.K. Sharma (@_pksharma) on X

Thread distinguishing two Langflow advisories on MCP Stdio command execution. CVE-2026-105740 (GHSA-7w94-79vh-5mr2) affects 1.8.3 and is fixed in 1.9.0, an authenticated non-admin path. CVE-2026-105697 (GHSA-w794-rj3p-xv45) covers 1.1.2 up to but excluding 1.10.3, with fixes in lfx and langflow-base too. The later fix validates the API, flow and pre-spawn boundaries and removes the shell wrapper, and the thread warns that LANGFLOW_AUTO_LOGIN=true can expose a token without credentials. It cites one sensor's telemetry (1,628 attempts from 28 IPs) with caveats, and gives a defensive checklist: verify patched packages, review stored MCP configs and imported flows, and hunt for unexpected child processes.

LangflowModel Context Protocol
CVE-2026-105740CVE-2026-105697GHSA-7w94-79vh-5mr2+4

AppSec, AI Security· Added 17 Oct 2026, published 15 Oct 2026

arxiv.orgpaper🛡️ Security

My Credentials, Please: Detecting Filesystem Capability Laundering in MCP Servers at Scale

Studies "filesystem capability laundering" in MCP servers: client approval of a tool call grants the server process broad host filesystem access, so attacker-steered arguments can reach sensitive files outside the tool's declared contract. The authors build MCP-FSD, which infers per-tool least-privilege boundaries, plants credential fixtures outside them, and tests exploitability and sandbox containment by paired dynamic execution. Of 21,097 servers from nine registries, 16.4% of 4,806 triaged servers have filesystem capabilities despite non-filesystem classifications. Dynamic validation confirmed 150 vulnerable instances, and disclosure produced 13 advisories, including two CVEs in Anthropic's Git MCP Server.

Model Context ProtocolAnthropicGit
filesystem capability launderingMCP-FSDpath traversal+1

AI Security, AppSec· Added 17 Oct 2026, published 15 Oct 2026

tldrsec.comarticle🛡️ Security

[tl;dr sec] #350 - Reverse Engineer Anything, Tracking AI-integrated Malware, Test-driving Jev

tl;dr sec issue #350 is a weekly security newsletter digest. It covers XBOW's six-day Chrome full-chain exploit built with GPT-5.6 Sol, Semgrep's IDOR benchmark metrics, the EntraGoat vulnerable Entra ID lab, Zenity's AWS Bedrock AgentCore IMDS credential theft, Cisco Talos's CAIRN hunting toolkit for AI-integrated malware, the REA reverse-engineering MCP, runZero's sshamble, and a Copilot for Word AI worm.

XBOWChromeMicrosoft Entra ID+3
EntraGoatAgentCorruptionCAIRN+11

AI Security, Offensive Security, Cloud & Infra· Added 30 Oct 2026, published 15 Oct 2026

x.comthread🛡️ Security

Francis Santerre (@santerref) on X

Post announcing that the MCP Adapter (0.7.0) is now a canonical plugin on WordPress.org, bridging the WordPress Abilities API to MCP. It exposes a default server at /wp-json/mcp/mcp-adapter-default-server, and only abilities a site marks public are exposed. The author's point is that the security review reduces to auditing the list of public abilities, which gives reviewers and pentesters a new endpoint to enumerate.

WordPressModel Context Protocol
MCP AdapterAbilities API/wp-json/mcp/mcp-adapter-default-server

AppSec, AI Security· Added 16 Oct 2026, published 15 Oct 2026

x.comthread🧠 AI

Francis Santerre (@santerref) on X

Tweet announcing that the MCP Adapter is now a canonical plugin on WordPress.org (version 0.7.0). It bridges the WordPress Abilities API to the Model Context Protocol, with a default server at /wp-json/mcp/mcp-adapter-default-server. Only abilities a site marks public are exposed, so the security review comes down to auditing the ability list.

Model Context ProtocolWordPressMCP Adapter+1
Abilities API

mcp· Added 16 Oct 2026, published 15 Oct 2026

x.comtool🛡️ Security

dbugs (@ptdbugs) on X

Decepticon is an open-source framework that automates red team operations with 16 specialized AI agents coordinated by an orchestrator, covering recon, vulnerability research and exploitation against an operator-authorized target in an isolated environment. It offers optional attack planning mapped to MITRE ATT&CK, persistent interactive sessions for Metasploit, Sliver and Evil-WinRM, and findings stored in project files and a knowledge graph. It runs via CLI or web dashboard, integrates with Claude Code and Codex through an MCP server, and is self-hosted with Docker Compose.

MetasploitClaude CodeCodex+3
DecepticonBitterSecurityEvil-WinRM+1

Offensive Security, AI Security· Added 18 Oct 2026, published 15 Oct 2026

arxiv.orgpaper🛡️ Security

Approve What, Exactly? Effect Binding and Trusted Rendering for Agent Step-Up Authorization

Paper arguing that agent human-approval prompts count as a second factor only if agent compromise cannot forge them and they name exactly what is approved. It defines twelve attacks on the approval path (decoy recipients, amount cancellation, card padding, label spoofing, enrollment squatting, threshold splitting) and tests them against AP2, Microsoft's action-bound approval design and MCP elicitation. An audit of ten agent runtimes found no third-party verifiable approval record and post-approval argument changes in four of eight. The reference defense ASU (Agent Step-Up) renders the card from a canonical effect descriptor, has a phone passkey sign its digest, and executes only the stored call. It is proven in Tamarin (53 lemmas) and evaluated on 27,108 scripted trials and 609 AgentDojo pairs. The trusted card cut forged-narration attack success from 0.54 to 0.03 and raised LLM-approver catch rate from 0.30 to 0.98.

Model Context ProtocolMicrosoft
Agent Payments ProtocolAgent Step-UpASU+6

AI Security, Identity & Access· Added 17 Oct 2026, published 15 Oct 2026

decrypt.coarticle🧠 AI

Developer Who Cloned Photoshop With AI Just Did the Same to Microsoft Office

Decrypt reports that developer Brandon Thomas released WordCraft, GridCraft and DeckCraft, MIT/Apache-2.0 open-source clones of Word, Excel and PowerPoint. They were written in Rust with Anthropic's Claude (Opus 5.5) as a clean-room rebuild and run natively on Windows, macOS, Linux and BSD, and in a browser. Coverage is high (WordCraft 88% of ribbon features, GridCraft 513 of 523 Excel functions), but the authors rate them only about 50–60% ready for real work. Every button is also an MCP command, so agents like Claude can drive the apps. The article is a useful data point on what AI-assisted "vibe coding" can produce in under two weeks, and on where it still falls short (file fidelity, stability).

RustClaudeModel Context Protocol+4
Brandon ThomasWordCraftGridCraft+10

coding-agents, mcp· Published and added 14 Oct 2026

arxiv.orgpaper🧠 AI

Thinking in Graphs: Neo4j-Backed Exploit-Chain Reasoning for LLM Penetration-Testing Agents

ChainGraph is a pattern that moves exploit-chain reasoning out of the flat context window and into a Neo4j property graph. Findings, attack steps, credentials, assets and tamper-evident evidence receipts are typed nodes with pre/post-condition edges. The graph is wired to Claude Code or Codex through MCP with no custom harness. Five operator questions (next-step inference, entry-to-crown-jewel pathing, combined-severity promotion, evidence provenance, chokepoint identification) become reusable Cypher and Graph Data Science queries, plus a chain-severity score. On a synthetic multi-forest Active Directory lab modeled on GOAD, three findings rated Medium in isolation become Critical once their path to the forest root is materialized. Scoping each decision to a graph result cut the reasoning payload by about 98% on a token proxy. The authors say the results are illustrative single-run measurements, not a benchmark.

Neo4jModel Context ProtocolClaude Code+4
ChainGraphGOADarXiv

agents, mcp, research· Added 17 Oct 2026, published 14 Oct 2026

x.comthread🛡️ Security

Victor (@VMG_CU) on X

A social post summarising Elastic's REF8801 campaign. A fake startup accelerator offered founders free Claude/Gemini credits plus a coding agent. The agent was a repackaged open-source project that set OPENROUTER_BASE_URL to an attacker-controlled endpoint and added its own MCP server, so victims' prompts and code went to the attacker. It shows how a trojanised AI coding agent can hijack the LLM base URL and add an MCP server for exfiltration.

OpenRouterModel Context ProtocolClaude+1
REF8801Elastic Security LabsOPENROUTER_BASE_URL

Threat Intel, AI Security· Added 15 Oct 2026, published 14 Oct 2026

github.comrepo🧠 AI

Show HN: Graphicle, a Rust port of Graphify with memory for coding agents

Graphicle is a local-first Rust program that parses a repository into a tree-sitter code graph (a port of Graphify) and adds project memory: docs, reviewed decisions and captured Claude Code/Codex sessions. It serves cited file-and-line excerpts within a token budget via one MCP server, CLI and browser app, backed by a single SQLite file, with no API key or telemetry. The README reports a code-only extract on Kubernetes (31k files) in 3m18s versus 26m38s for Graphify 0.9.88, and a memory comparison against seven systems. Agent-proposed memories need user approval and go stale when the code they reference changes.

RustModel Context ProtocolSQLite+12
GraphicleGraphifyKarLex AI+2

coding-agents, mcp, llm-apps· Published and added 14 Oct 2026

x.comtool🧠 AI

Francesco Sorrentino (@Fr_Sorrentino) on X

chrome-bridge is an open-source MCP server with a Chrome extension that lets Claude Code drive the user's own Chrome, including logged-in tabs and DevTools. It reads page structure rather than screenshots, which saves tokens and turns. The author reports gains over Claude in Chrome: 4.7× fewer turns and 2.8× lower cost on form filling, 2.3× and 3.4× on finding a row among 1,500, and 9.3× and 4.3× on debugging a broken checkout, with 15/15 correct against 12/15. These are self-reported numbers from the tweet.

Model Context ProtocolClaude CodeChrome+1
chrome-bridgeClaude in ChromeAnthropic

mcp, coding-agents· Published and added 14 Oct 2026

github.comrepo🧠 AI

morluto/rea

REA (rea-agents on npm) registers an MCP server and matching workflow instructions with coding agents such as Claude Code, Codex, Cursor and Gemini CLI. It exposes tools for inspecting native binaries through Hopper, Ghidra or IDA (with optional objdump and Rizin), JavaScript/Electron apps and ASAR archives, .NET assemblies and websites. Results come back with evidence and limitations, so the agent can explain how a feature works and write and test its own implementation. Analysis runs locally, there is a CLI with the same workflows, and the showcases include C reconstructions verified against original x86 function bytes.

Model Context ProtocolClaude CodeCodex+14
REAIDA

mcp, coding-agents· Added 14 Oct 2026

github.comrepo🛡️ Security

morluto/rea

REA (rea-agents) is an MIT-licensed toolkit that exposes native-binary, JavaScript/Electron, .NET assembly and website analysis to AI agents via MCP, and also as a local CLI. It drives Hopper, Ghidra, IDA, objdump or Rizin for disassembly and pseudocode, recovers modules and Electron IPC boundaries from ASAR/JS apps, and returns findings with evidence and limitations. Showcases include reconstructing a x86 audio helper into byte-matching C and tracing an Electron clipboard API through preload and IPC; the README also carries lawful-use and licensing guidance.

Model Context ProtocolGhidraHopper+3
REArea-agentsASAR

Malware & RE, AI Security· Added 14 Oct 2026

x.comthread🧠 AI

44er (@44errrr) on X

Announcement of hexvero, an MCP server that gives coding agents a static first look at binaries and app bundles across 18 formats (ELF, PE, Mach-O, APK, .NET, Go, Wasm, Electron, SQLite). It uses zero-dependency Node parsers and marks each finding confirmed or inferred with file and line. Its tool catalog is 3,043 tokens, against a claimed 509,696 for the established reverse-engineering MCP server. Paged output with a byte budget shrinks a 541 MB Electron app to a 15 KB result, 1.3 MB of JSON to 7.9 KB, and a 450 KB build diff to 1.2 KB. radare2, rizin or Ghidra plug in for disassembly, and `npx hexvero setup --apply` registers it with Claude Code, Cursor, Codex and 15 more clients. It is a concrete example of keeping MCP tool definitions and results small enough for an agent's context window.

Model Context ProtocolNode.jsnpm+12
hexvero

mcp, coding-agents· Added 15 Oct 2026, published 14 Oct 2026

x.comtool🛡️ Security

44er (@44errrr) on X

hexvero is a Node-only, zero-dependency MCP server that gives coding agents a static first-look triage of binaries and app bundles across 18 formats (ELF, PE, Mach-O, APK, .NET, Go, Wasm, Electron, SQLite). Findings are marked confirmed or inferred with file and line, and outputs are paged with a byte budget (a 541 MB Electron app yields a ~15 KB result). The author contrasts its 3,043-token tool catalog with a 509,696-token catalog of an established RE MCP server. radare2, rizin or Ghidra can be plugged in for disassembly, and setup registers it with Claude Code, Cursor, Codex and 15 more clients.

Model Context ProtocolGhidraNode.js+3
hexvero

Malware & RE, AI Security· Added 15 Oct 2026, published 14 Oct 2026

embracethered.comwriteup🛡️ Security

Visual Studio Copilot and SSMS Remote Code Execution (CVE-2026-103572)

CVE-2026-103572 is a remote code execution bug in Microsoft.VisualStudio.Copilot.Core.dll, shared by Visual Studio and SQL Server Management Studio. A trailing dot (for example `.mcp.json.`) bypasses the protected-filename check in EditsFunctionHandler.GetEditConfirmationTypeAsync, so a hijacked Copilot can rewrite its own MCP and settings files and run commands. The post covers path traversal and InstallationID leaks, indirect prompt injection demos, the October 2026 patch (GetFullPath), and a $0 bounty.

Visual StudioSQL Server Management StudioGitHub Copilot+3
CVE-2026-103572indirect prompt injectionpath traversal+5

AI Security, AppSec, Offensive Security· Added 29 Oct 2026, published 13 Oct 2026

ethereum-magicians.orgthread🧠 AI

ERC-8444: Agentic Resource Discovery (ARD) Onchain

An Ethereum Magicians proposal for ERC-8444, which adds an onchain value and settlement layer under Google's Agentic Resource Discovery (ARD) spec for finding MCP servers, A2A agents, skills and APIs. A thin kernel records kind (skill, task, agent, registry), a CAIP-19/CAIP-10 anchor, a JCS+SHA-256 descriptor hash, a canonical URN and a status. Authority belongs to the paid address, and domains act as collected endorsements through /.well-known/ard.json. The reference implementation has Foundry-tested Solidity adapters and a Node.js gateway that passes the official ARD conformance CLI. It introduces a "task" kind (application/ai-task+json) for tenders aimed at suppliers, and the author asks for feedback on the trust root, the hash scope, same-chain anchors and the task payload.

Model Context ProtocolEthereumSolidity+2
GoogleMicrosoftHugging Face

mcp, agents· Added 14 Oct 2026, published 13 Oct 2026

pdftomp3.comtool🧠 AI

Show HN: Use your OpenAI subscription to create audiobooks

PDF TO MP3 is a hosted MCP server (Streamable HTTP, account authentication) that turns PDFs into audiobooks. The user's existing AI subscription, such as Codex, handles document processing through the MCP connection. Speech generation is billed separately through the user's own OpenAI or Google text-to-speech API key. The setup is three steps: add the MCP server, add a speech key, then attach a PDF and ask the assistant to use the MCP. It shows a "bring your own subscription" pattern that keeps the vendor's compute costs low.

Model Context ProtocolCodexOpenAI API+1
PDF TO MP3OpenAIGoogle

mcp, multimodal· Published and added 13 Oct 2026

linkedin.comarticle🧠 AI

AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples

A guided tour of a GitHub repository of resources and examples for building AI agents, published on the Becoming a Hacker blog. Per the routing note, it covers LangChain 1.x, LCEL, RAG, LangGraph, CrewAI, DeepAgents, MCP servers and token-cost control such as caching, routing and budget guards. The fetched page held only a LinkedIn redirect notice, so the article text was not read.

LangChainLangGraphCrewAI+4

agents, llm-apps, mcp· Added 13 Oct 2026

becomingahacker.orgarticle🧠 AI

AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples

Guided tour of Omar Santos's eight-part AI-agents-for-cybersecurity repository. It moves from LLM building blocks (LangChain, RAG) to security agents built with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan). It also covers a hardening guide for six agentic frameworks, token-cost control, and a spec for a supervisor-led, human-gated assessment harness. Design lessons include least-privilege subagents, single-use approvals and kill switches.

LangChainRAGLangGraph+7
Omar SantosOWASPCISA+1

agents, mcp, llm-apps· Added 13 Oct 2026

github.comrepo🧠 AI

santosomar/AI-agents-for-cybersecurity

Companion repository for Omar Santos's Pearson and O'Reilly trainings and books. It has eight parts of runnable Python labs: chat models, embeddings, prompt templates, LCEL prompt chaining, Chroma-based RAG, ReAct/LangGraph/CrewAI/DeepAgents agents, and FastMCP servers (nmap, CISA KEV, Shodan). It also includes guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz), a tokenomics module on agent cost (context compounding, prompt caching, model routing, token budget guards, batch API, cost per accepted outcome), and a vendor-neutral design spec for a human-gated multi-agent assessment harness. It is a current, practical curriculum for building and operating agents. Some examples act on real systems and should only be run in an authorized lab.

PythonuvLangChain+17
Omar SantosPearsonO'Reilly+15

agents, llm-apps, mcp· Added 13 Oct 2026

github.comrepo🛡️ Security

santosomar/AI-agents-for-cybersecurity

Omar Santos's companion repo for his Pearson/O'Reilly trainings and books, organised in eight parts. They cover LangChain prompts, chains and RAG (Chroma), and agents (LangGraph, CrewAI, DeepAgents). They also cover FastMCP security servers (nmap, CISA KEV, Shodan) and attack-surface-management and SOC agent examples. Later parts have security guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz) with hardening notes and 2026 CVE mapping, agent cost/tokenomics scripts including denial-of-wallet budget guards, and a vendor-neutral spec for a human-gated multi-agent security-assessment harness (scope manifest, approval gates, kill switch). Useful as a hands-on path into AI-agent security tooling, with warnings that some examples act on real systems.

Model Context ProtocolLangChainOpenClaw+3
Omar SantosSSRFCISA KEV+2

AI Security, Learning· Added 13 Oct 2026

becomingahacker.orgarticle🛡️ Security

AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples

Omar Santos walks through his eight-part AI-agents-for-cybersecurity repository: LLM building blocks (LangChain, RAG), then security agents with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan), a hardening guide for six agentic frameworks, token-cost control for agents, and a spec for a supervisor-led, human-gated security-assessment harness. It covers concrete design lessons such as least-privilege subagents, staged response actions, single-use approvals bound to exact actions, kill switches, and mapping controls to the OWASP Top 10 for Agentic Applications. Also notes Project CodeGuard rules shipped for AI coding assistants.

LangChainModel Context ProtocolPython+3
Omar SantosProject CodeGuardOWASP Top 10 for Agentic Applications+5

AI Security, Learning, Blue Team & Detection· Added 13 Oct 2026

linkedin.comarticle🛡️ Security

AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples

Omar Santos walks through his AI-agents-for-cybersecurity GitHub repo, which has eight parts. Parts 1–4 cover LLM basics (LangChain, prompting, LCEL, RAG). Parts 5–8 cover building security agents with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan), and a hardening baseline for six ready-made agentic frameworks. They also cover token-cost control (caching, routing, budget guards, cost per accepted outcome) and a supervisor-led, human-gated security-assessment harness spec with single-use approvals, a kill switch and an append-only audit log. The post also covers Project CodeGuard rules for AI coding assistants. It is a practical learning path and a reference for governing and securing agents.

LangChainLangGraphCrewAI+5
Omar SantosProject CodeGuardOWASP Top 10 for Agentic Applications+9

AI Security, Learning, Blue Team & Detection· Added 13 Oct 2026

github.comrepo🧠 AI

Show HN: SolidCraft – Open-Source Parametric CAD in Rust (With MCP Support)

SolidCraft is an open-source parametric 3D CAD application written in pure Rust. It has constrained sketches with its own solver, a feature timeline, assemblies, sheet metal, and STEP/IGES/3MF/STL export. It runs on desktop (egui+wgpu), in the browser, and as a headless CLI. The built-in MCP server (`solidcraft-cli mcp`) gives agents tools such as execute, batch, inspect_design, measure, set_parameter, screenshot and export. They can model headless or drive the running app over a JSON-lines control channel. A rover with 3,323 timeline steps was built entirely through MCP, which shows agent-driven parametric modelling working at scale.

RustModel Context ProtocolClaude Code+5
SolidCraftSELENE

mcp· Published and added 13 Oct 2026

decrypt.coarticle🧠 AI

From GTA V on iPhone to Free Photoshop: This AI Tool Is Upending Software

Decrypt reports on REA (Reverse Engineer Anything), an open-source toolkit that uses MCP to connect AI coding agents such as Claude Code and Codex to reverse-engineering tools like Ghidra. It went from under 10,000 to over 100,000 GitHub stars in a week. The article describes AI-decompiled game ports and mashups, and ArtCraft, a set of Rust-built Photoshop-style apps that Brandon Thomas made with Claude Opus 5.5 as a clean-room rebuild. It also covers the copyright and takedown fallout (Activision, Bethesda) and what cheap agent-driven decompilation means for software protection.

Model Context ProtocolClaude CodeCodex+3
REAClaude Opus 5.5Anthropic+7

coding-agents, mcp, ai-policy· Published and added 12 Oct 2026

x.comthread🛡️ Security

Phillip Shoemaker (@pbsIdentity) on X

Social thread reacting to a newly disclosed high-severity OAuth vulnerability in the Model Context Protocol Python SDK, where a malicious MCP server could manipulate the authorization flow and steal credentials used by an agent. The author uses it to argue that delegated agent authority needs provenance (who granted it, to which agent, for which service and resource, whether it is transferable or replayable, and when it expires) and that machine-to-machine trust must be auditable by humans. Gives no CVE ID or technical exploit detail.

Model Context ProtocolPythonOAuth
confused deputy

AI Security, Identity & Access· Added 13 Oct 2026, published 12 Oct 2026

github.blogarticle🧠 AI

GitHub Copilot app for Beginners: How to teach Copilot about your codebase

Beginner-oriented GitHub blog guide to giving GitHub Copilot project context through four mechanisms: repository custom instructions (.github/copilot-instructions.md and path-specific .github/instructions files with applyTo), agent skills (SKILL.md folders under .github/skills), custom agents (.github/agents profiles), and MCP servers such as Playwright. It explains when to use each and how they combine, using examples like a quality-checks skill and an accessibility-review agent. Useful as a concrete reference for the repo layout Copilot reads, with a pointer to the community Awesome Copilot collection.

GitHub CopilotModel Context ProtocolPlaywright+1
Awesome Copilot

coding-agents, prompting, mcp· Published and added 12 Oct 2026

jfrog.comarticle🧠 AI

Governing the Agentic SDLC Through Continuous Policy Enforcement

JFrog proposes the Agentic Process Evidence Protocol, an open spec that records coding-agent sessions (harness and agent version, model ID, tool and MCP calls, prompts, owner, human reviewer) as signed in-toto/DSSE attestations bound to a git commit, artifact or release. Policy-as-code release gates can then check for approved LLMs and MCP tools, an accountable human and adherence to guidelines, and the logs allow post-release audit. The post gives mock session-log and evidence JSON, ties the approach to EU AI Act Articles 12 and 14, OWASP AISVS and SLSA, and points to a GitHub reference repo, with JFrog AppTrust as the commercial implementation.

CursorOpenCodeClaude Code+8
JFrogJFrog AppTrustAgentic Process Evidence+8

ai-policy, coding-agents· Added 14 Oct 2026, published 12 Oct 2026

jfrog.comarticle🛡️ Security

Governing the Agentic SDLC Through Continuous Policy Enforcement

JFrog proposes Agentic Process Evidence, an open protocol that records AI coding agent sessions (harness, model ID, tool calls, MCP use, prompts, owner, human reviewer) as signed in-toto/DSSE, SLSA-compatible attestations bound to commits, artifacts and releases. Policy-as-code gates can then block releases that used unapproved LLMs or MCP tools, or that lack an accountable human. It maps the approach to EU AI Act Articles 12/14, OWASP AISVS and ISO/IEC 42001, and includes example session-log and evidence JSON. The post also promotes JFrog AppTrust's Prompt to Release Traceability.

JFrogin-totoCursor+3
Agentic Process EvidenceAppTrustPrompt to Release Traceability+8

AI Security, DevSecOps, Supply Chain· Added 14 Oct 2026, published 12 Oct 2026

endorlabs.comarticle🛡️ Security

The OWASP Top 10 Gets Modernized | Endor Labs

Commentary on the 2025 OWASP Top 10 update presented at OWASP Global AppSec in Washington, D.C. Broken Access Control stays #1, Security Misconfiguration and the new Software Supply Chain Failures category (replacing Vulnerable and Outdated Components) rise to #2 and #3, and Cryptographic Failures, Injection and Insecure Design drop. The author adds context on agentic AI and MCP identity and authorization, AI-assisted SAST, non-human identities, CISA Secure-by-Default, OWASP SPVS, and slopsquatting and AI coding assistant risks.

Model Context Protocol
OWASPOWASP Top 10 2025Broken Access Control+8

AppSec, Supply Chain· Published and added 12 Oct 2026

endorlabs.comarticle🧠 AI

Context Engineering for Application Security | Endor Labs

Endor Labs whitepaper on using context engineering to make AI coding assistants produce secure code. It covers secure prompting (priming, decomposition, refinement with design-spec and test-first patterns), reusable system rules such as Cursor rules and the CSA R.A.I.L.G.U.A.R.D. framework, and external SAST/SCA tools wired in through MCP servers with a rule that triggers scans. It also covers the costs and risks: extra token use, models ignoring rules, untrusted community rules, and MCP server supply-chain threats. It cites figures such as 62% of AI-generated solutions containing flaws and a 77.5% reduction in weaknesses from recursive prompting.

CursorModel Context ProtocolClaude+1
Endor LabsOWASPCloud Security Alliance

prompting, coding-agents, llm-apps· Published and added 12 Oct 2026

endorlabs.compaper🛡️ Security

State of Dependency Management 2025 | Endor Labs

Endor Labs' 2025 State of Dependency Management report examines how AI coding agents and MCP servers add supply chain risk. Researchers analysed 10,663 GitHub MCP server repositories and tested AI-generated dependency recommendations across PyPI, npm, Maven and NuGet, finding agents import vulnerable or non-existent packages. MCP servers are immature: 75% are built by individuals, 41% lack license info, and 82% use sensitive APIs. The report advises treating AI-generated code as untrusted third-party input subject to code review, SAST/SCA and dependency governance.

Model Context ProtocolGitHubPyPI+3
Henrik Plate

Supply Chain, AI Security· Published and added 12 Oct 2026

Showing 120 of 508

Show more