Skip to content

1210 results for β€œGo”

What you seeeverything
newsletter.semianalysis.comarticle🧠 AI

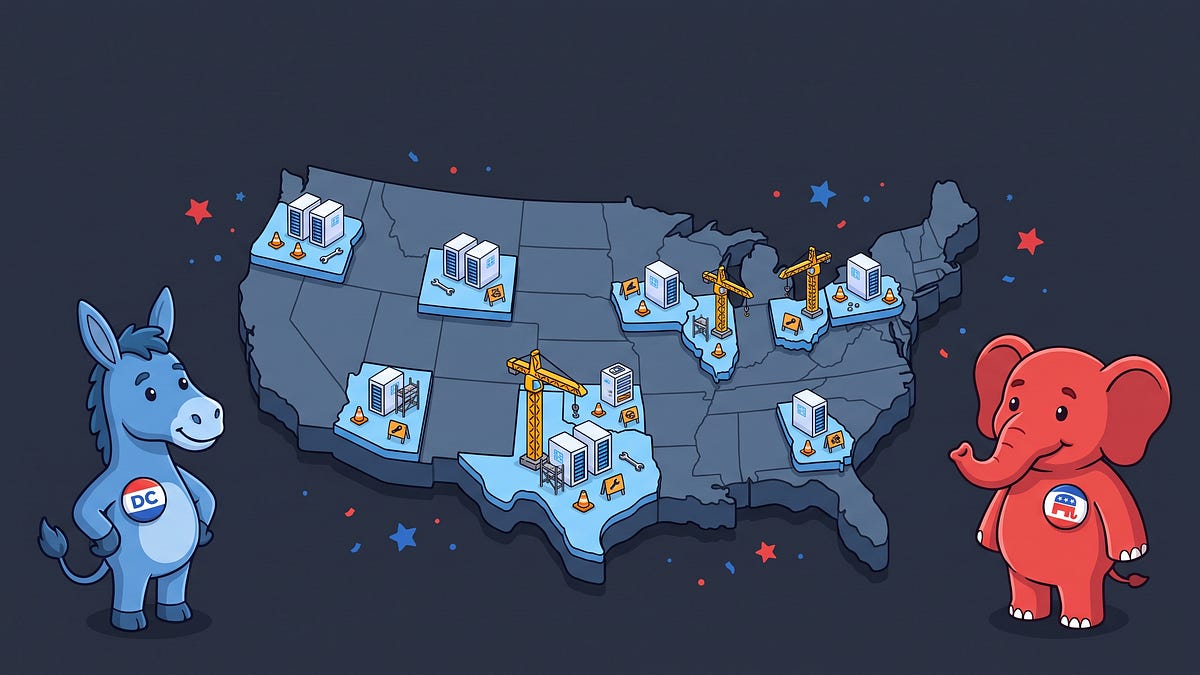
The Datacenter Backlash Goes Bipartisan: Next Week's Midterms and the 2028 Buildout

SemiAnalysis analysis of how the November 2026 US midterms could affect datacenter buildout. About 75% of the 33.8 GW due in 2027 across the top 20 states is already under construction, but 43.5 GW of 2028 additions sit in 13 states with pending approvals. The biggest risk is a prolonged Texas TCEQ permit freeze. Texas holds close to 30% of 2028 GW, and nine of 20 nominees back a pause.

SemiAnalysisTexas Commission on Environmental QualityERCOT+16

ai-policyΒ· Published and added 1 Nov 2026

x.comthread🧠 AI

Prasenjit Sarkar (@stretchcloud) on X

Campfire is a free, open-source, self-hosted tool that runs Claude Code, Codex, Goose, Aider and OpenHands side by side in one browser tab. Each agent gets its own git worktree, with permission voting (30 second timer, majority rules), session replay, cross-backend agent races and a shared semantic memory layer. Installs with bunx the-campfire. The post also compares Clawboo, Conductor, Vibe Kanban and Crystl.

CampfireClawbooClaude Code+8
Boo ZeroConductorVibe Kanban+2

agents, coding-agentsΒ· Added 1 Nov 2026, published 31 Oct 2026

bleepingcomputer.comarticleπŸ›‘οΈ Security

Northflank security breach leads to abuse of customers' AI API keys

Northflank, a cloud application hosting platform, disclosed a breach on 30 October 2026 after a Wiz threat alert and told customers to assume all environment variables were decrypted and to rotate secrets. Customers reported unauthorized use of AI API keys. Wiz's "Black October for AI Developer Platforms" report counts at least nine incidents, including Railway, OpenCode, Warp and Lightning AI, and describes LLMJacking, with about 2.5 million Amazon Bedrock calls costing roughly $100,000 in two cases. Northflank has not said how attackers got in.

NorthflankWizAWS Bedrock+3
LLMJackingBlack October for AI Developer PlatformsRailway+2

Threat Intel, AI Security, DevSecOpsΒ· Published and added 31 Oct 2026

bleepingcomputer.comarticleπŸ›‘οΈ Security

New Android SMS of Death exploit can remotely crash unpatched phones

CVE-2026-58882, "SMS of Death", is a zero-click Android denial-of-service flaw in WapPushOverSms.decodeWapPdu, where an unchecked header-length value becomes negative and triggers a NegativeArraySizeException that crashes com.android.phone. A malformed eight-byte WAP Push message to port 2948 can drop calls, including emergency calls, and about 20 messages caused reboot loops. A PoC is public. Google patched Android 14 through 17 in October 2026, but Android 12 and 13 remain vulnerable.

AndroidAndroid Debug BridgeGitHub
CVE-2026-58882SMS of DeathGoogle+3

Mobile Security, Offensive SecurityΒ· Published and added 31 Oct 2026

x.comarticle🧠 AI

Lewis - Policifyai (@Policifyai) on X

Policifyai's October 2026 roundup lists model releases by date with prices and benchmark scores: GPT-6.1 Sol and Terra, Claude Sonnet 5.5 and Haiku 5.5, Gemini 4 Argon and Carbon, Muse Spark Open, Mistral Large 4 weights and Kimi K3.1 Pro. It also covers Anthropic's S-1 compute commitments, Artificial Analysis Intelligence Index v5, and chip and data-center deals.

CodexHugging FaceMixture of Experts+6
OpenAIAnthropicGoogle+43

models, ai-infra, evalsΒ· Added 1 Nov 2026, published 31 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Syrian Hacker Gets Prison Time in US After Over a Decade on the Run

Ahmad Umar Agha (Th3Pr0), a Syrian Electronic Army member, received a 42-month US sentence in the Eastern District of Virginia, over 12 years after he was first charged in June 2014. He compromised about 47 Western media, company, NGO and government targets, including the 2013 Associated Press Twitter takeover that caused a flash crash. Accomplice Firas Dardar remains at large.

Twitter
Syrian Electronic ArmyAhmad Umar AghaTh3Pr0+5

Threat IntelΒ· Published and added 31 Oct 2026

latent.spacearticle🧠 AI

[AINews] Google admits AI Mode hurts Search revenue; -15% $500B drop worst since 2004 IPO. AI Bear Market coming?

AINews issue for 29 to 30 October 2026 from Latent Space. It opens on Google's admission that AI Mode monetises worse than classic Search, which preceded a roughly 15% share drop. It then recaps Claude Ultra dropping the 5-hour limit, Gemini 4 Carbon, Mistral Large 4, Nemotron 3.5, Artificial Analysis Index v5, Unsloth GGUF disputes, and the Anthropic S-1 filing.
Claude CodeClaudeGemini+17
GoogleAnthropicOpenAI+46

ai-policy, models, evalsΒ· Published and added 31 Oct 2026

huggingface.copaper🧠 AI

Your Benchmark Is an Empirical Measure Over Difficulty

The paper treats a benchmark as an empirical measure over item difficulty and formalizes two failure modes: measure mismatch (benchmark difficulty distribution differs from the intended one) and coverage gaps (uncovered difficulty regions that hide localized training progress). It proposes two diagnostic metrics with theoretical guarantees and analyzes 25 popular benchmarks across 7 domains using estimated item difficulties. It also introduces BenchFill, a difficulty-targeted item rewriting algorithm that reduces local coverage gaps.

BenchFill

evals, researchΒ· Added 31 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

ClioBitcoinBank πŸ΄β€β˜ οΈ (@ClioBitcoinBank) on X

lnd v0.20.7 and v0.21.6 are Lightning Network Daemon releases announced by Clio Bitcoin Bank. They include a Go-specific mitigation, with the MPTCP flag turned off, for CVE-2026-98432, a use-after-free in the Linux kernel's IPv4 TCP code. The post recommends all users update. It gives no exploit or impact detail.

lndLinux kernelGo+2
CVE-2026-98432use-after-freeClio Bitcoin Bank

Cloud & InfraΒ· Published and added 31 Oct 2026

bleepingcomputer.comarticleπŸ›‘οΈ Security

Critical Linux kernel flaw allows remote root attacks on MPTCP servers

CVE-2026-98432 is a use-after-free race condition in the Linux kernel IPv4 TCP code (tcp_v4_syn_recv_sock, ireq_opt), affecting kernels back to 4.4 and rated 9.8 by the kernel CVE team (Red Hat rates it 5.9). Anthropic researchers say an unreleased Claude model built an exploit that bypassed KASLR and got remote root on an MPTCP listener in about 53 minutes. The article lists distro patch status and CIQ's nftables mitigation for IP options; disabling MPTCP alone does not help. No in-the-wild exploitation is reported.

Linux kernelAnthropicClaude+2
CVE-2026-98432use-after-freeKASLR bypass+4

Offensive Security, AI Security, Cloud & InfraΒ· Published and added 30 Oct 2026

galaxy.comarticleπŸ›‘οΈ Security

Here We Go Again: Binance Loses $6.3b in Largest Robbery in History

Galaxy Research newsletter on the roughly $6.3b drained from Binance across 10 blockchains, which TRM Labs and Chainalysis attribute to TraderTraitor. On Ethereum the attacker used EIP-7702 to turn a hot wallet into a sweeper contract backed by 50 pre-signed authorizations. Binance's preliminary finding is a compromised DevOps laptop, with no wallet key leak. Tether, Circle, Ripple and World Liberty froze about $2.7b; Galaxy also assesses Binance's ability to cover losses.

EthereumBitcoinTether+3
TraderTraitorLazarus GroupBinance+7

Blockchain, Threat IntelΒ· Added 30 Oct 2026

blog.cloudflare.comwriteupπŸ›‘οΈ Security

4 real? Tracking exploitation and patching of eMudhra’s weak keys

Cloudflare's follow-up on eMudhra's eight trivially recoverable intermediate CA keys (such as 4, 56 and 66), disclosed 19 October 2026. Pingora logging showed about 22,000 handshakes with the weak keys, including about 160 forged certificates made within hours of disclosure. Probes on 50 million challenge pages show many bots, old browsers and Android WebView still trust the chain.

CloudflarePingoraAndroid WebView+2
eMudhraMozillaDennis Jackson+6

Threat Intel, Blue Team & DetectionΒ· Published and added 30 Oct 2026

blog.googlearticle🧠 AI

We’ve received our first response from the Project Suncatcher prototype satellite.

Project Suncatcher is a Google research effort to power AI compute in space. Its prototype satellite launched on 1 October 2026 and, after commissioning, returned the first AI response from a data-center-class TPU in orbit: a haiku from the onboard Gemma 4 open model, downlinked over Svalbard. Next come thermal-stress and radiation tests, then twin interconnected satellites in 2027.

TPUGemma
GoogleGemma 4Project Suncatcher+1

inference, ai-infraΒ· Published and added 30 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

In Other News: Anthropic Breach Dispute, UEFI Flaw Hits Most Servers, Cloudflare AI Data Leak

SecurityWeek's weekly roundup of 30 October 2026 covers CVE-2026-97631, a 16-year-old buffer overflow in TianoCore EDK II that affects PXE network boot on most servers. It also covers a Cloudflare Workers AI cross-tenant leak caused by an SGLang bug, Anthropic's dispute with Cathedral over a bug bounty intrusion, and fake AI bots probing for secrets. Other items include AI-assisted ransomware (Gold Ogre, Aur0ra), the NIK C2 framework, and North Korean IT worker sanctions.

TianoCore EDK IISGLangCloudflare Workers+3
CVE-2026-97631CathedralCequence+9

Threat Intel, AI Security, Hardware & RFΒ· Published and added 30 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Passkeys Are Better Than Passwords. But They Are Not Enough.

Opinion piece arguing that passkeys, built on public-key cryptography, resist phishing, credential stuffing and password theft but do not settle identity risk. Attackers can go around them through account enrollment before a passkey is bound, weaker recovery paths (SMS, email link, help desk), device changes and authenticated session hijacking. It proposes layering identity threat detection with risk-based, continuous evaluation of trust.

passkeysMFA
adversary-in-the-middleMFA fatigueSIM swapping+3

Identity & AccessΒ· Published and added 30 Oct 2026

cloud.google.comarticleπŸ›‘οΈ Security

ARTEX and Friends: Enter Agentic Offensive Frameworks

ARTEX is an open-source, Go-based multi-agent LLM pentesting and C2 platform that Google Threat Intelligence Group and Mandiant saw threat actors run in incident response cases from late August 2026, alongside PentAGI and CAIRN. The report covers ARTEX behaviour such as MySQL general_log JSP webshell poisoning and burst timing, UNC7228 (overlapping STORM-0940), a seven-stage model of adversary LLM use, and five Mandiant defensive layers. The text was truncated before the last layers.

GoNext.jsLLM+3
ARTEXPentAGICAIRN+14

Threat Intel, AI Security, Offensive Security, Blue Team & DetectionΒ· Added 1 Nov 2026, published 30 Oct 2026

cyberplace.socialthreadπŸ›‘οΈ Security

Backdoors in official Claude Code extensions

GossiTheDog's Mastodon post reports that the Anthropic Claude Code Visual Studio extension, as installed in Cursor, contains malware that creates a remote access Trojan on desktops. It links to a phorion.io blog post on the reported compromise of the official Claude Code VSX extension. The post gives no technical detail, indicators or dates itself.

Claude CodeCursorOpen VSX+1
Anthropicremote access Trojan

Supply Chain, Threat IntelΒ· Added 31 Oct 2026, published 30 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

$2 Million+ Drained From Polymarket Traders in New Supply Chain Attack

Polymarket halted trading on 29 October after users reported unauthorized withdrawals traced to malicious JavaScript served from DebugBear's real user monitoring snippet. Hudson Rock's sample abused the authenticated session to sell positions or send tokens to a hard-coded address, without exfiltrating credentials. Loss estimates range from $2.19 million to $2.71 million (GoPlus), and Polymarket pledged reimbursement.

PolymarketDebugBearJavaScript
Hudson RockGoPlusArkham+2

Supply Chain, Threat IntelΒ· Published and added 30 Oct 2026

x.comthreadπŸ›‘οΈ Security

ESET Research (@ESETresearch) on X

ESET Research thread summarising its APT Activity Report for April to September 2026 on Russia-aligned groups targeting Ukrainian defense, government and infrastructure. Gamaredon deployed Turla's new VBScript recon tool Rezzuar, indicating FSB-linked collaboration, and updated its file stealer PteroBox while activity fell sharply from mid-May. A separate campaign hit MDaemon mail servers via CVE-2025-8088, delivering HELLAGE and HELLTAG backdoors with no user interaction.

MDaemonClamAVWinRAR+1
CVE-2025-8088GamaredonTurla+6

Threat IntelΒ· Added 31 Oct 2026, published 30 Oct 2026

ethereum-magicians.orgotherπŸ›‘οΈ Security

ERC draft: Independent Simulation Result for (STVA)

ERC draft "Independent Simulation Result" (STVA) defines a canonical, content-addressed SimulationResult structure that wallets, hardware devices or third-party verifiers can recompute from the same VerificationPayload and state snapshot. It specifies fields, a keccak256 or EIP-712 result hash, and Basic, Standard and Strict compliance tiers. The goal is to close UI/calldata mismatch attacks where a compromised frontend serves a false simulation. Open questions cover stateDiff encoding and prestate proofs.

EthereumrevmSafe
ERC-7730Scoped Capability TokensUI/calldata mismatch+5

BlockchainΒ· Published and added 30 Oct 2026

vulncheck.comtoolπŸ›‘οΈ Security

VulnCheck - Outpace Adversaries

VulnCheck Open Source is an index of VulnCheck's open-source tooling for its vulnerability and exploit intelligence. It lists a Python API client, a CLI, a GitHub Action for CI/CD, go-exploit (a Go exploit framework), an MCP server for delivering intelligence to AI clients, and VulnCheck Insights, a Chrome extension that highlights CVEs, CPEs and PURLs on web pages and enriches them. The page gives only one-line descriptions.

GoPythonGitHub Actions+2
VulnCheckgo-exploitVulnCheck Insights+2

Offensive Security, DevSecOpsΒ· Added 29 Oct 2026

oversecured.comwriteupπŸ›‘οΈ Security

Discovering vendor-specific vulnerabilities in Android | Oversecured Blog

Oversecured describes extending its Android scanner to system APIs and to Samsung's Android build, after comparing Google and Samsung framework JARs and about 400 system services. It explains AIDL service permission checks and new control-flow analyses. Examples include Samsung's unchecked semIsBackupEnabled(), a broadcast that reboots the device, and a LaunchAnyWhere in Settings. Samsung had fixed over 60 reported issues.

AndroidSamsungOversecured
LaunchAnyWhereAIDLsystem_server+1

Mobile Security, AppSecΒ· Added 29 Oct 2026

oversecured.comarticleπŸ›‘οΈ Security

Content Providers and the potential weak spots they can have | Oversecured Blog

Oversecured's Android security checklist for Content Providers covers insecure FileProvider path configs, path traversal via decoded Uri.getLastPathSegment(), mismatched readPermission/writePermission, proxying requests to more privileged providers, SQL injection across a shared database, and sensitive actions in providers. Each case has vulnerable manifest and Java code, an attacker PoC and remediation. Real cases from Google and Samsung devices are cited. The page text was truncated near the end.

AndroidSQLiteJava
Oversecuredpath traversalSQL injection+5

Mobile Security, AppSecΒ· Added 29 Oct 2026

oversecured.comarticleπŸ›‘οΈ Security

Oversecured Apps Care. Part 1: Vulnerability disclosure of 225 Google apps | Oversecured Blog

Oversecured Apps Care, Part 1 (21 March 2024) publishes scanner results for about 224 Google Android apps, drawn from a wider scan of over 6,000 public APKs from 1,000+ companies. Tables per device image (phone, Wear OS, Android Automotive, Android TV) give package names, three finding counts and report links, including android, com.android.settings, gms and Play Store. It invites researchers to report issues to Google for rewards.

AndroidWear OSAndroid Automotive+1
OversecuredOversecured Apps Care

Mobile Security, AppSecΒ· Added 29 Oct 2026

oversecured.comwriteupπŸ›‘οΈ Security

Disclosure of 7 Android and Google Pixel vulnerabilities

Oversecured discloses seven Android vulnerabilities, two of them Pixel-specific, all reported to Google and fixed except one low-severity WebView case. They are the Camera geolocation leak (CVE-2024-0017), a VPN bypass list change (CVE-2023-21383), a Bluetooth permission check flaw (CVE-2024-34719), the WorkSource parcel mismatch (CVE-2023-20963, exploited in the wild by the Pinduoduo app), Device Admin HTML injection (CVE-2021-0600) and a ContentProvider.openFile() caller-context bypass (CVE-2023-21292). Each has root cause and PoC code.

AndroidGoogle PixelWebView+2
CVE-2024-0017CVE-2023-21383CVE-2024-34719+9

Mobile Security, Offensive SecurityΒ· Added 29 Oct 2026

oversecured.comarticleπŸ›‘οΈ Security

Inside mobile taint analysis: how source-to-sink tracking finds real data-leak paths | Oversecured Blog

Oversecured explains taint analysis for Android and iOS apps and contrasts it with pattern-matching SAST such as MobSF. It covers source, flow and sink, cross-component tracking over Intents, flag-based sanitizer modeling and implicit intent simulation. The case study is an unsafe Class.forName().newInstance() on a Serializable transportFactoryClassName field in Google's com.google.auth.oauth2 credential classes, which Google fixed with a $3,133.70 bounty.

AndroidiOSOversecured+3
intent redirectionpath traversalSSRF+4

Mobile Security, AppSecΒ· Added 29 Oct 2026

oversecured.comarticleπŸ›‘οΈ Security

Vulnerabilities that lead to account takeover in banking and fintech mobile apps | Oversecured Blog

Oversecured guide to eight vulnerability categories that lead to account takeover in mobile banking and fintech apps: WebView JavaScript bridge token leakage, Intent Redirection, hardcoded tokens, deeplink hijacking, insecure token storage, localhost OAuth listeners, AIDL abuse and weak biometric auth. It includes a WebView PoC based on Samsung SmartThings CVE-2022-30746 and maps findings to OWASP MASVS, PCI DSS and PSD2. It argues taint analysis plus dynamic PoC is needed to find multi-component chains.

AndroidiOSOAuth+1
CVE-2022-30746Intent Redirectiondeeplink hijacking+9

Mobile Security, AppSec, Identity & AccessΒ· Added 29 Oct 2026

x.comthread🧠 AI

Prasenjit Sarkar (@stretchcloud) on X

A thread on Cloudflare's agent-readiness scan and the AgentReady.org open spec for "Agent Experience", developed with Vercel, Stripe, Auth0, Mintlify, Google, Netlify and Elementor. The scan grades whether agents can find a site (robots.txt, DNS), read clean Markdown, pass bot rules, and discover an MCP server or API catalog. One quoted example raised a score from 20 to 67 by shipping an API catalog with Link headers, an MCP server card, a skills index and an AI catalog file.

Model Context ProtocolCloudflareMarkdown
AgentReady.orgOraNick Launches+7

mcp, agentsΒ· Added 30 Oct 2026, published 29 Oct 2026

blog.talosintelligence.comarticleπŸ›‘οΈ Security

A quiet week in infosec <.<

Cisco Talos Threat Source newsletter for the week of the PHP and Node.js vulnerability news cycle. It summarises NIK C2, a Go-based Windows implant that dumps credentials, streams keystrokes, deploys screen-locking ransomware and uses a victim's hijacked OpenAI API keys to analyse stolen data. It also lists weekly headlines (CISA KEV PHP bugs, Brotli flaw, Gheist GitHub token theft), Talos links and top malware hashes.

GoWindowsOpenAI+3
NIK C2PHP2ShellNode2Shell+7

Threat Intel, AI SecurityΒ· Published and added 29 Oct 2026

arxiv.orgpaper🧠 AI

Retrieving from Your Own Mistakes: On-Policy Training of Embedding Models for Multi-Hop Retrieval-Augmented Generation

On-policy state training is a method for training chain embedding retrievers for multi-hop RAG on the states the encoder itself reaches, including those built on its own wrong retrievals. Each state is labeled with the earliest missing gold passage, other missing gold passages are masked, and updates are contrastive and mixed with teacher-forced states. It retrieves complete evidence more often than teacher-forced training and graph-based systems, and transfers to harder long-chain HotpotQA and 2WikiMultiHopQA variants the authors built.

RAGon-policy state trainingcontrastive learning+1
HotpotQA2WikiMultiHopQAarXiv

research, llm-apps, trainingΒ· Added 31 Oct 2026, published 29 Oct 2026

arxiv.orgpaper🧠 AI

Don't Lose the Thread: Empowering Long-Horizon LLM Agents with Cognitive Resource Self-Allocation

CORAL (Cognitive Resource Self-Allocation) is an agent-callable working-memory toolset that lets an LLM agent checkpoint task progress and verified facts, then reset its cluttered context and resume from a clean state. A Multi-episode Agentic Reinforced Policy Optimization algorithm trains the checkpointing. With an 8B model it reaches 42.8% average accuracy on GAIA, uses 6-7x fewer input tokens than a ReAct agent, and adds 8.0 points to a proprietary agent on BrowseComp.

LLMReActCORAL
Multi-episode Agentic Reinforced Policy OptimizationGAIABrowseComp

agents, research, trainingΒ· Added 31 Oct 2026, published 29 Oct 2026

arxiv.orgpaper🧠 AI

Decompose, Estimate, Select: Coverage-Aware Context Construction for Long-Form RAG

Decompose, Estimate, Select is a coverage-aware retrieval pipeline for long-form RAG. It splits a query into subquestions, ranks candidates with a coverage-trained bi-encoder, predicts a document-by-subquestion coverage matrix with a cross-encoder, and picks documents by greedy maximum-marginal coverage. On TREC RAG 2024, Ξ±-nDCG@10 rises from 0.625 to 0.702 (gold-nugget bound 0.718). A grounded self-feedback loop raises V_strict by 0.086 over two passes.

RAGbi-encodercross-encoder+1
TREC RAG 2024Ξ±-nDCG@10V_strict

llm-apps, researchΒ· Added 31 Oct 2026, published 29 Oct 2026

securityweek.comarticle🧠 AI

Google Touts Powerful Cybersecurity Capabilities in Gemini 4 Carbon Model

Gemini 4 Carbon is Google's new frontier model, announced with scores of 88.2% on SEC-bench Pro, 54.8% on ExploitGym and 71.0% on CWE-bench. Google says it beats GPT-6 Astra, Claude Opus 5.5 and Claude Fable 5.1 on these, with no guardrails. Access is limited to Fairwind Program partners at first. Pricing starts at $2 input and $10 output per million tokens, rising to $4 and $20.

Gemini
GoogleGemini 4 CarbonGemini 4 Argon+13

models, evalsΒ· Published and added 29 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Google Touts Powerful Cybersecurity Capabilities in Gemini 4 Carbon Model

Gemini 4 Carbon is a Google frontier model announced with restricted access for cyber defenders through the Fairwind Program (650+ organizations). Google reports 88.2% on SEC-bench Pro, 54.8% on ExploitGym and 71.0% on CWE-bench, ahead of GPT-6 Astra and Claude models, with no guardrails. It also cites prompt injection and cheating-resistance results, and pricing of $2/$10 per million tokens.

GeminiGPT-6 AstraWiz+1
Gemini 4 CarbonGemini 4 ArgonFairwind Program+6

AI SecurityΒ· Published and added 29 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

Quasi-polynomial time algorithms for block basis reduction of linear codes

Kolesnikov and Novoselov give block basis reduction (BKZ) algorithms for linear codes that need polynomial or quasi-polynomial numbers of calls to a minimum weight codeword oracle at fixed block size. The earlier Ghentiyala and Stephens-Davidowitz bounds are exponential. The paper adds a truncated BKZ and a DeepBKZ variant, with an implementation for block sizes 2 to 24 and approximation-factor estimates on random codes.

BKZDeepBKZminimum weight codeword problem+4

otherΒ· Added 31 Oct 2026, published 29 Oct 2026

blog.talosintelligence.comwriteupπŸ›‘οΈ Security

NIK C2: The new AI-enabled command-and-control framework

NIK C2 is a newly observed C2 framework with a Go-based 64-bit Windows implant that embeds an OpenAI Chat Completions client (ai_generate command), falling back to the victim's OPENAI_API_KEY. Talos details its 52+ commands, AES-256-GCM over WebSocket with HTTP fallback, credential, wallet and keystroke theft, screen-lock ransomware, AMSI bypass and anti-debug. It also lists a live C2 at 87.120.196[.]120 and total-sitevv[.]lol.

GoOpenAIWindows+3
NIK C2nik_panel87.120.196[.]120+9

Malware & RE, Threat Intel, AI SecurityΒ· Published and added 29 Oct 2026

aikido.devarticleπŸ›‘οΈ Security

Ghost in the PHP2Shell: Why coordinated disclosure and patching will start moving faster

Aikido's analysis of the PHP2Shell disclosures (CVE-2026-109618 and CVE-2026-109619), published October 2026. It covers the timeline: the CVE IDs leaked on 20 October, PHP moved its release to 21 October, and Amazon reports exploitation attempts from 17 October. It cites Censys data (32.5 million services still affected on 27 October) and argues that AI-driven discovery and exploit building call for shorter embargoes and faster patching.

PHPAikido SecurityCodex+2
CVE-2026-109618CVE-2026-109619PHP2Shell+8

AI Security, AppSecΒ· Added 28 Oct 2026, published 29 Oct 2026

blog.googlearticle🧠 AI

How Gemini is helping students and teachers in the classroom

Google reports two classroom studies of Gemini. In a 10-week RCT with over 1,100 UK students (ages 12-15) on Eedi, Gemini-based AI tutoring matched human tutors on in-platform tasks and quizzes, with expert approval of responses rising from 76% to 95%. Gains did not appear on STAR standardized tests. A yearlong Italian study of 1,600 teachers found lessons co-designed with Gemini shifted toward collaborative work.

GeminiGemini for Education
GoogleEediSTAR+3

research, evals, ai-policyΒ· Added 30 Oct 2026, published 29 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

HHS Filing Puts iRhythm Data Breach Toll at 8.2 Million

The June 2026 iRhythm data breach is now listed on the HHS breach portal as affecting 8,179,772 people, the same figure given to the Oregon Attorney General. Attackers took data from third-party-hosted business applications, including names, addresses, birth dates, contact details, and account, serial and insurance numbers, and tried to extort a ransom. iRhythm reports no impact on its products or clinical systems and offers no free credit monitoring.

iRhythmHHSHIPAA+2

Threat IntelΒ· Published and added 29 Oct 2026

latent.spacearticle🧠 AI

[AINews] Gemini 4 Carbon tops leaderboards, launches for cyber defenders

AINews issue for 27-28 October 2026, a Latent Space digest of Twitter and Reddit. It leads with Google DeepMind's Gemini 4 Carbon: claimed cyber scores (SEC-bench Pro 88.2%, ExploitGym 54.8%, CWE-bench 71.0%), #1 on Artificial Analysis Intelligence Index v5 at 59, and access limited to cyber defenders through the Fairwind Program. It also covers benchmark integrity disputes, GitHub Copilot Fusion, H-Net v2, KV-cache work, open-weight releases and Claude Code quota complaints.

GeminiClaude CodeGoogle Antigravity+12
Gemini 4 CarbonGemini 4 ArgonGoogle DeepMind+39

models, evals, coding-agentsΒ· Published and added 29 Oct 2026

endorlabs.comarticleπŸ›‘οΈ Security

ADLC metrics: How to measure agentic development security | Endor Labs

ADLC metrics is an Endor Labs guide to measuring security in the agentic development lifecycle, where AI coding agents write much of the code. It defines formulas across five categories: AI supply chain visibility, agent action security, agent-generated code, package risk and developer flow. It argues for normalizing findings per merged change, tracking pre-execution blocks, and building a six-to-eight metric scorecard.

Claude CodeCodexCursor+3
ADLCOWASP Top 10 for LLM ApplicationsAgent Security League+4

AI Security, AppSec, DevSecOpsΒ· Published and added 29 Oct 2026

endorlabs.comarticle🧠 AI

ADLC metrics: How to measure agentic development security | Endor Labs

ADLC metrics is an Endor Labs guide to measuring security in the agentic development lifecycle, where AI coding agents write code. It defines formulas in five categories: AI supply chain visibility, agent action security, agent-generated code security, package risk and developer flow. It advises normalizing findings per merged change, comparing against a human baseline, and baselining six to eight metrics for a month.

Claude CodeCodexCursor+4
Endor LabsAURIOWASP+4

coding-agents, ai-policyΒ· Published and added 29 Oct 2026

socket.devwriteupπŸ›‘οΈ Security

Searchjacked: Hidden Browser Extensions Hijack Searches for 13 Million Users

Searchjacked is Socket's research on 319 browser extensions (about 13.44M users over a decade) that hijack searches to earn ad revenue. The fetched text attributes 200 extensions to named operators such as Intango, System1, Perion, Mutual Media and Kinner Lake, and 119 to unknown operators like "SecuryBrowse" and "Bing-Search". It lists the Yahoo and Bing monetization IDs used to link them. The narrative and technical mechanics are not in the fetched text.

Chrome Web StoreChrome
SearchjackedIntangoLumio+20

Threat Intel, Supply ChainΒ· Published and added 29 Oct 2026

arxiv.orgpaper🧠 AI

DICE: Decentralized Incentive-driven Federated Learning for Efficient & Scalable Customization of Pretrained Models in Web3

DICE is a blockchain-powered federated learning (BCFL) algorithm for customizing large pretrained models among untrusted Web3 participants. It combines dynamic progressive learning and model slice verification, so hardware-limited participants can train part of the model, with a tree-structured committee consensus protocol and an efficiency-driven incentive scheme to scale to more data holders. Experiments cover vision and language models.

federated learningblockchain-powered federated learningprogressive learning+1
arXiv

research, trainingΒ· Added 31 Oct 2026, published 29 Oct 2026

securitylabs.datadoghq.comwriteupπŸ›‘οΈ Security

Node2Shell: Reproducing CVE-2026-111497 in the Node.js Brotli decoder

Node2Shell is Datadog Security Labs' analysis of CVE-2026-111497, an out-of-bounds write in the Google Brotli 1.2.0 decoder, fixed in Node.js 22.23.4, 24.22.1 and 26.12.1 on 21 October 2026. It explains the unchecked return value in DecodeBlockTypeAndLength(), the read and write primitives, and why code execution is still engineering effort. It lists inbound and outbound exposure paths, behavioral detections and what WAFs miss.

BrotliNode.jsBun+3
CVE-2026-111497Node2ShellCISA KEV+3

AppSec, Blue Team & Detection, Offensive SecurityΒ· Published and added 29 Oct 2026

bleepingcomputer.comarticleπŸ›‘οΈ Security

Police seize Virtualine bulletproof service tied to ransowmare, cybercrime

Virtualine, a bulletproof hosting service also operating as Secury, Massgod, Spamhouse, Lanedo and Omegatech, had its main domain seized by the FBI with German, Dutch and UK partners. Chainalysis and TRM Labs traced its Bitcoin payments to ransomware (5% of flows), a Russian drug market (about 44%), sextortion and the StealC infostealer. Dutch police seized dozens of servers in Limburg and recovered data on over 3,000 customers.

Bitcoin
VirtualineSecuryMassgod+14

Threat IntelΒ· Added 30 Oct 2026, published 28 Oct 2026

arxiv.orgpaper🧠 AI

Gold vs.~Translation: Are We Measuring Language, Knowledge, or Locality in Translated Benchmarks?

Gold vs. Translation is an October 2026 arXiv study of whether DeepL-translated MMLU measures the same thing as native benchmarks. It compares seven pairings against six native benchmarks in five Nordic and Baltic languages, using 29 models. Translated MMLU adds predictive value for curriculum-overlap benchmarks such as Skolprov (Ξ”RΒ²=.128) but not for Sweden-specific SwedishFacts (p=.242).

LLM
MMLUDeepLSkolprov+2

evals, researchΒ· Added 30 Oct 2026, published 28 Oct 2026

decrypt.coarticle🧠 AI

OpenAI Plans to Buy Google's AI Chips as It Looks Beyond Nvidia: Report

Decrypt reports, citing The Information, that OpenAI plans to buy Google TPUs rather than rent them, to reduce dependence on Nvidia. Neither company has confirmed, and price, volume and timing are undisclosed. The article covers OpenAI's TPU optimization job listing, its Broadcom-built JalapeΓ±o inference chip due end of 2026, Nvidia and AMD deals, and Anthropic's multi-gigawatt TPU agreement.

TPUJalapeΓ±oGoogle Cloud
OpenAIGoogleNVIDIA+10

inference, ai-infraΒ· Published and added 28 Oct 2026

x.comthread🧠 AI

Laban (@lunkertw) on X

An X post summarising five AI items: Google DeepMind's Gemini 4 Carbon (88.2% SEC-bench Pro, 54.8% ExploitGym, 71.0% CWE-bench, 59 on Artificial Analysis Intelligence Index v5.0), Ed Zitron's critique of Anthropic's S-1, a Utah Claude Code pilot, and the repos beenuar/AiSOC and expo/skills. In the Utah pilot, 34 developers in 10 agencies took part over four weeks, 80% had a working setup within 30 minutes, and 71% saved over 20 hours. It gives short summaries and links, not primary analysis.

Claude CodeModel Context ProtocolPython+6
Google DeepMindGemini 4 CarbonSEC-bench Pro+9

models, coding-agents, ai-policyΒ· Added 29 Oct 2026, published 28 Oct 2026

arxiv.orgpaper🧠 AI

AskStream: When and What to Ask Proactively under Uncertainty in Streaming Video Understanding

AskStream is a multi-turn benchmark for streaming video understanding that adds a third proactive action, ask, alongside wait and answer, for cases where video or user information is incomplete. It has 438 videos, 2,714 manually annotated frame-level time windows (wait, ask, answer), four task categories and eight subtasks. The strongest model reaches only 52.18% on the proposed Ask-F1 metric, in both multiple-choice and open-ended settings.

multimodal large language model
AskStreamAsk-F1arXiv

evals, multimodal, researchΒ· Added 30 Oct 2026, published 28 Oct 2026

x.comthread🧠 AI

Niko (@nikolayxyz) on X

Gemini 4 Carbon is Google's new frontier model, announced in a post by nikolayxyz that quotes Google's launch text. It ranks #1 on v5.0 of the Artificial Analysis Intelligence Index with 59 points, ahead of Opus 5.5 and GPT-6 Astra. Intro pricing is $2 input and $10 output per million tokens. Access starts for cyber defenders first, as Gemini 4 Argon's did. The captured text is cut off before the rollout details.

Gemini
Gemini 4 CarbonGemini 4 ArgonGoogle+4

models, evalsΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comthread🧠 AI

🚨 AI News | TestingCatalog (@testingcatalog) on X

Gemini 4 Carbon is a new Google model, announced in a TestingCatalog post on X as taking first place on the Artificial Analysis V5 ranking. It is rolling out to cyber defenders first. Reported scores are 88.2% on SEC-bench Pro (finding vulnerabilities), 54.8% on ExploitGym (exploitation) and 71.0% on CWE-bench (patching). The post calls it a large step up from Gemini 4 Argon, released two weeks earlier. It gives no technical detail beyond these claims.

Gemini
GoogleGemini 4 CarbonGemini 4 Argon+4

models, evalsΒ· Added 30 Oct 2026, published 28 Oct 2026

blog.googlearticleπŸ›‘οΈ Security

Gemini 4 Carbon

Gemini 4 Carbon is Google's frontier model, announced with cybersecurity results: 88.2% on SEC-bench Pro (finding vulnerabilities), 54.8% on ExploitGym (exploitation) and 71.0% on CWE-bench (patching). Google reports 0.0% attack success on Gray Swan's indirect prompt injection benchmark. Access starts with a subset of cyber defenders through the Fairwind Program. Pricing is $2 per million input tokens and $10 per million output tokens.

Gemini
Gemini 4 CarbonGemini 4 ArgonFairwind Program+6

AI SecurityΒ· Added 29 Oct 2026, published 28 Oct 2026

blog.googlearticle🧠 AI

Gemini 4 Carbon

Gemini 4 Carbon is Google's frontier model, announced two weeks after Gemini 4 Argon. It scores 59 on Artificial Analysis Intelligence Index v5.0, 88.2% on SEC-bench Pro, 54.8% on ExploitGym and 71.0% on CWE-bench. Pricing is $2 per million input and $10 per million output tokens. Access starts with a subset of cyber defenders through the Fairwind Program.

Gemini
Gemini 4 CarbonGemini 4 ArgonGoogle+10

models, evals, ai-safetyΒ· Added 29 Oct 2026, published 28 Oct 2026

deepmind.googlearticleπŸ›‘οΈ Security

Gemini 4 Carbon: Our next frontier model

Gemini 4 Carbon is Google DeepMind's frontier model, announced with a focus on cyber defense. DeepMind reports 88.2% on SEC-bench Pro (finding vulnerabilities), 54.8% on ExploitGym (exploitation) and 71.0% on CWE-bench (patching), run without guardrails. It also reports 0.0% attack success on Gray Swan's indirect prompt injection benchmark. Access starts with a subset of cyber defenders via the Fairwind Program.

Gemini
Gemini 4 CarbonGemini 4 ArgonSEC-bench Pro+6

AI Security, AppSecΒ· Published and added 28 Oct 2026

deepmind.googlearticle🧠 AI

Gemini 4 Carbon: Our next frontier model

Gemini 4 Carbon is Google DeepMind's new frontier model, announced two weeks after Gemini 4 Argon. It ranks #1 on Artificial Analysis Intelligence Index v5.0 at 59 and scores 88.2% on SEC-bench Pro, 54.8% on ExploitGym and 71.0% on CWE-bench. Access starts with cyber defenders through the Fairwind Program, priced at $2 per million input tokens and $10 per million output tokens.

Gemini
Gemini 4 CarbonGemini 4 ArgonGoogle DeepMind+12

models, evals, ai-safetyΒ· Published and added 28 Oct 2026

decrypt.coarticle🧠 AI

House Oversight Chair Comer Probes Delaware Plan for AI-Run Companies

House Oversight Chairman James Comer opened an investigation on 26 October 2026 into Delaware's proposed Artificial Intelligence Company (AIC), a legal entity run day-to-day by an AI agent. His letter to Gov. Matt Meyer requests documents, including internal AI chat logs, by 9 November. The AIC would run in a 30-month sandbox with a single member shielded from debts, and Delaware's draft legislation is expected in January 2027.

James ComerHouse Oversight CommitteeMatt Meyer+8

ai-policyΒ· Published and added 28 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

TLS Flaws Found in GoAhead Web Server Used in Hundreds of Millions of Devices

FoxIO disclosed three TLS flaws in the GoAhead embedded web server from EmbedThis, used on hundreds of millions of IoT, OT and network devices. CVE-2026-115881 (CVSS 9.1) leaves revoked client certificates accepted under mTLS with OpenSSL; CVE-2026-115884 (7.4) bypasses chain-length limits with LibreSSL; a third Mbed TLS bug (5.9, no CVE) weakens TLS 1.2 DHE. GoAhead 6.1.1 fixes the OpenSSL and Mbed TLS issues, and FoxIO released PoC code and fingerprints.

GoAheadOpenSSLMbed TLS+2
CVE-2026-115881CVE-2026-115884FoxIO+4

Hardware & RF, AppSecΒ· Published and added 28 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

Shor's algorithm compiled on cat qubits: 22 593 qubits for RSA-2048 in 3.14 days

Shor's algorithm compiled on cat qubits is an IACR ePrint (2026/2665) giving an end-to-end resource estimate on superconducting cat qubits, using repetition and LDPC cat codes. Factoring RSA-2048 needs about 23,000 cat qubits and 3.14 days, assuming phase-flip noise p_Z = 5e-4 and no bit-flips. secp256k1 ECDLP needs at most 30,000 qubits and 1 hour. A space-for-time trade runs RSA-2048 in 1.25 hours on about 611,000 qubits.

Bitcoin
Shor's algorithmRSA-2048secp256k1+5

otherΒ· Published and added 28 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

China-Linked Hackers Exploit PHP2Shell to Root Firewalls

A China-linked actor chained PHP2Shell (CVE-2026-109618, CVE-2026-109619) with the Fragnesia Linux kernel privilege escalation (CVE-2026-46300) to root firewalls and drop PHP webshells, per Dream. Using FOFA, the actor narrowed 19,000 firewalls to 240 targets and rooted 24 on 23-24 October. On two US government-affiliated devices it used a reverse SSH tunnel, hit the firewall management server, and attempted LDAP and Active Directory abuse.

PHPLinux kernelSSH+2
CVE-2026-109618CVE-2026-109619CVE-2026-46300+7

Threat Intel, Offensive SecurityΒ· Published and added 28 Oct 2026

akamai.comarticleπŸ›‘οΈ Security

TLP Is Not a Suggestion

Akamai SIG argues that vendors and researchers broke embargo norms during the October 2026 PHP2Shell leak, when the PHP fix shipped a day early on 21 October. It explains the four TLP 2.0 labels, tabulates past embargo breaks (Heartbleed, a collapsed six-month kernel-era embargo, the Alibaba Cloud and MIIT case), and lists seven practices, such as no proofs of concept or CVE numbers before the fix.

PHP
CVE-2026-111497PHP2ShellTraffic Light Protocol+11

otherΒ· Added 30 Oct 2026, published 28 Oct 2026

arxiv.orgpaper🧠 AI

CALM: Conflict-Aware Lifecycle Memory Governance for Long-Horizon Language Agents

CALM is a conflict-aware lifecycle memory governance framework for long-horizon language agents. It turns records into evidence-grounded memory cells, updates their validity and lifecycle states from support, conflict and dependency signals, and admits evidence at query time through training-free or learned gating based on temporal applicability. It beats baselines on LongMemEval-S and LoCoMo with Qwen and GPT backbones, and keeping superseded records helps earlier-state reasoning.

LLMQwen
CALMLongMemEval-SLoCoMo+1

agents, researchΒ· Added 30 Oct 2026, published 28 Oct 2026

endorlabs.comarticleπŸ›‘οΈ Security

How to evaluate ADLC security solutions: A buyer's checklist | Endor Labs

Buyer's checklist from Endor Labs for evaluating security tools in the agentic development lifecycle (ADLC), where AI coding agents write code and take actions such as package installs, CI edits and tool calls. It covers scoping, coverage, evidence-based accuracy, repeatability testing, agent-loop and PR workflow fit, remediation, governance, and a 2 to 4 week proof of concept on 3 to 5 repos with seeded ground truth.

Endor LabsAURIModel Context Protocol+3
ADLCIDORNIST SSDF+1

AppSec, AI Security, DevSecOpsΒ· Published and added 28 Oct 2026

arxiv.orgpaper🧠 AI

Complementing Text Based Moderation with Multimodal Grounding: Detecting Fraudulent Inducement Behaviors on Short Video Platforms

The paper studies detection and temporal localization of fraudulent inducements (prompts to follow, join chat groups, click links) in internet finance short videos. It compares OCR+LLM, OCR+MLLM and a zero-shot MLLM, and builds a dataset of 2,419 videos (66.49 hours, 3,194 events, four categories). OCR+MLLM reaches mIoU 26.52 versus 14.49 for keyframe OCR+LLM, with 67.0 percent macro recall, using a recall-weighted F2 localization reward.

MLLMLLMOCR
arXiv

research, multimodal, trainingΒ· Added 30 Oct 2026, published 28 Oct 2026

huggingface.copaper🧠 AI

What Effort Level Should I Choose? On the Economics of Reasoning Effort in LLM Agents

This paper treats LLM reasoning effort as a credence good and measures the counterfactual effect of effort levels on proprietary and open-weight models across four benchmarks, including long-horizon agentic tasks. Higher effort often fails on tasks lower effort solved, and on easy tasks the top level costs up to 42x the lowest. Starting at the lowest effort and escalating only after a verified failure matches or beats fixed top effort, usually at lower cost for proprietary models.

LLM
Hugging Face

research, evals, agents, ai-policyΒ· Added 28 Oct 2026

chainalysis.comarticleπŸ›‘οΈ Security

International Law Enforcement Seizes Domain of Virtualine Bulletproof Hosting Service

Virtualine is a bulletproof hosting provider whose domain virtualine.net was seized on 27 October 2026 by the FBI Washington Field Office and the Eastern District of Virginia, with German, Dutch and UK police support. Chainalysis and OverRIPE gave intelligence support. The post lists aliases (Secury, Massgod, Spamhouse, Lanedo, Omegatech), forum advertising on Exploit.in and HackForums, and unhosted bitcoin payments tied to ransomware, infostealers and scam infrastructure.

BitcoinChainalysis Reactor
VirtualineSecuryMassgod+13

Threat IntelΒ· Published and added 27 Oct 2026

x.comthreadπŸ›‘οΈ Security

Kizuno18 (@Kizuno18) on X

Thread by Kizuno18 on the move from local stdio/Docker Model Context Protocol servers to remote HTTP/SSE endpoints in enterprise infrastructure. It names three trade-offs: credential boundary inversion (short-lived OAuth/JWT tokens instead of long-lived admin tokens on workstations), tool schema bloat solved by deferred discovery, and governance via HCP Terraform policy-as-code (Sentinel/OPA), audit trails and approvals. It is opinion, with no data or implementation detail.

Model Context ProtocolTerraformDocker+2
Sentinelblast radiuspolicy-as-code+1

AI Security, Identity & Access, DevSecOpsΒ· Added 29 Oct 2026, published 27 Oct 2026

brangus.iotool🧠 AI

Survival LLM: AI assistant and emergency library that runs on your own computer

Survival LLM is a free, open-source desktop app for macOS (Apple Silicon) and 64-bit Windows that runs an AI model and an offline emergency library on the user's computer. It checks the machine's memory, downloads a fitting model, and answers from sources such as Wikipedia, WikiMed, Ready.gov and CDC guidance, citing each article. Users can add their own files; version 0.3.2 is dated October 2026.

LLMRAGmacOS+1
Survival LLMWikipediaWikiMed+9

llm-apps, inferenceΒ· Added 28 Oct 2026, published 27 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA alert of 27 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities (KEV) Catalog on evidence of active exploitation: CVE-2026-48356, an unrestricted upload of a dangerous file type in Adobe Commerce and Magento, and CVE-2026-111497, an unchecked return value in Google Brotli. It restates BOD 26-04, which makes federal civilian agencies prioritise KEV flaws on exposed assets and check for prior compromise. No technical detail or IOCs are given.

Adobe CommerceMagentoBrotli
CVE-2026-48356CVE-2026-111497CISA KEV+2

AppSec, GRCΒ· Added 29 Oct 2026, published 27 Oct 2026

arxiv.orgpaper🧠 AI

Perceiving and Predicting Dynamic Sports: Spatiotemporal Intelligence in Vision Models for Egocentric Tennis Video

This paper presents an annotated egocentric tennis dataset (egocentric video synced with five allocentric views, global positions, contact times, stroke types) and evaluates image encoders, video encoders and vision-language models on seven prediction tasks. Best models reach 0.14 m player and 0.54 m ball localization error and 0.14 s contact-time error. Depth input helps 3D ball localization, and longer histories do not help forecasting. A conditional diffusion model generates whole-body tennis motion in real time.

vision-language modeldiffusion modelTransformer
arXiv

research, multimodal, evalsΒ· Added 28 Oct 2026, published 27 Oct 2026

hackers-arise.comarticleπŸ›‘οΈ Security

Pentesting: Twelve Caesars – Community Tools for Offensive Security

Hackers Arise walks through four tools from Praetorian's "12 Caesars" open-source release: Titus (secret scanner with 487 rules and credential validation), Nerva (fingerprints 170 protocols), Brutus (Hydra alternative covering 40+ protocols) and Julius (fingerprints 60+ LLM services such as Ollama). It shows download and run commands in a Kali lab and how the tools chain together. The tools are Go single binaries; the post notes an exposed Ollama on port 11434 allows unauthenticated model use.

GoKali LinuxOllama+3
Praetorian12 CaesarsTitus+4

Offensive Security, DevSecOps, AI SecurityΒ· Published and added 27 Oct 2026

decrypt.coarticle🧠 AI

OpenAI Proves ETH Is False, and Crypto Twitter Has Questions

Decrypt reports that OpenAI published a 67-page paper (dated 17 October 2026, revised 25 October) claiming its AI found a deterministic subexponential-time algorithm for counting 3-SAT solutions, which would refute the Exponential Time Hypothesis. The proof was formalized in Lean. Impagliazzo, Paturi and Ryan Williams are reviewing it independently and say this is not certification. Anthropic posted a Claude-credited 3-SAT paper on 26 October.

LeanGitHubClaude
OpenAIAnthropicDecrypt+7

research, modelsΒ· Published and added 27 Oct 2026

deepmind.googlearticle🧠 AI

Genie 4: A new generation of world simulation

Genie 4 is Google DeepMind's real-time interactive world model, announced as a research preview for trusted testers. It generates video with native audio and interactive dialogue, steered by keyboard controls and text prompts. Gemini 3.8 Flash acts as a guiding agent that plans steps and checks frames, and Gemini 4 Argon is used for robotics experiments. The post lists limitations such as drift and object permanence, and says outputs carry SynthID watermarks.

GeminiGoogle AI StudioSynthID
Google DeepMindGenie 4Gemini 3.8 Flash+5

models, multimodal, agentsΒ· Published and added 27 Oct 2026

blog.googlearticle🧠 AI

We’re announcing Genie 4, our new world model for real-time interactive simulation.

Genie 4 is Google DeepMind's world model for real-time interactive simulation, with native audio generated on the fly (ambient sound, music, dialogue). It builds on Gemini models: Gemini Omni grounds scenes in real-world appearance and behavior, and other Gemini models keep the simulation coherent. Users steer scenes by natural language. Access is limited to trusted testers now, with Google AI Ultra (Project Genie), the Gemini API and AI Studio to follow. The post gives no architecture or benchmark detail.

GeminiGoogle AI StudioGemini API
Google DeepMindGenie 4Gemini Omni+2

models, multimodalΒ· Added 30 Oct 2026, published 27 Oct 2026

arxiv.orgpaper🧠 AI

Interpretable Meta-Policies for Neural Decision Making

NEXUS is a hierarchical reinforcement learning framework that pairs neural skills with symbolic meta-policies, so transparent reasoning sits at the level of high-level skills rather than atomic actions. It uses object-centric observations and LLM interaction to design reward functions and meta-policies. Agents learn disentangled skills, align better with goals in the game manual, resist reward hacking more, and cope better with game simplifications than deep RL. The paper also compares neural, symbolic and neuro-symbolic meta-policy architectures.

LLM
NEXUSarXiv

research, training, ai-safetyΒ· Added 28 Oct 2026, published 27 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

Radical isogenies on every model

Radical isogenies on every model is an IACR ePrint paper by Thomas Decru (October 2026). It gives radical isogeny steps of every odd degree N directly on short Weierstrass, Montgomery, twisted Edwards, Huff, Jacobi quartic, twisted Hessian, Legendre and Jacobi intersection curves, plus Kummer lines. In Tate normal form a step drops from 12.5N to 10N multiplications. Montgomery and twisted Edwards curves cost 10.5N+O(1) per step and 2N to push a point. All algorithms are inversion-free, with exact operation counts.

CSIDH
Thomas Decruradical isogeniesVΓ©lu's formulae+1

otherΒ· Added 28 Oct 2026, published 27 Oct 2026

privacy.claude.comarticle🧠 AI

Is my data used for model training?

Anthropic's privacy help article on whether customer data trains its models. For commercial products (Claude for Work, Anthropic API, Claude Gov), inputs and outputs are not used for training by default. Thumbs up/down feedback stores the whole conversation for up to 5 years, de-linked from user IDs, and may be used for training. Team and Enterprise owners can disable feedback in organization settings.

ClaudeModel Context ProtocolClaude Code
Anthropic

ai-policyΒ· Added 28 Oct 2026, published 27 Oct 2026

blog.cloudflare.comarticleπŸ›‘οΈ Security

What took the Internet offline in Q3 2026

Cloudflare's Q3 2026 review of the 49 Internet disruptions seen by Cloudflare Radar between July and September 2026. Government-directed shutdowns led with 19 (18 exam shutdowns in Iraq), followed by 14 power outages and 5 natural disasters. It gives traffic-drop figures and durations for Cuba, Honduras, Ukraine, Guam, Colombia, Ethiopia's Tigray region and others, including a Honduran interconnection facility power failure that cut HTTP traffic 63%.

Cloudflare
Iraq exam shutdownsTigray shutdownSuper Typhoon Bavi+10

otherΒ· Added 29 Oct 2026, published 27 Oct 2026

arxiv.orgpaper🧠 AI

LiveSearch: Questions as Executable Verifier Code for a Live Benchmark of Professional-Source Financial Search Agents

LiveSearch is a live benchmark for financial search agents that stores each question as executable verifier code: a typed program of calls to a professional financial data service plus a declarative extractor. Gold answers are recomputed daily with no human or LLM in the loop, so memorized answers go stale. Six tool-calling models score 70.9% to 76.7% under web search, and 70% of questions change gold value over three days.

LLM
LiveSearcharXiv

evals, agents, researchΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comthread🧠 AI

Rohan Paul (@rohanpaul_ai) on X

Hi3D v1.0 (formerly Sparc3D) is an open-sourced image-to-3D model from Hi3D, which runs a closed v3.0 refining at 2048 cubes per side. In a test with 13 professionals in 3D algorithms, 562 judgments against eight other image-to-3D models favoured it 83.5% of the time. The thread also covers the Hi3D Agent and an MCP server for other agents. Back and bottom views were checked, where TRELLIS.2 collapsed a winged figure.

Model Context Protocol
Hi3DHi3D v1.0Sparc3D+2

models, multimodal, mcpΒ· Added 28 Oct 2026, published 27 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

iOS, macOS 27.2 Patch 286 Bugs; Fix for Exploited Flaw Backported to iOS 18

Apple's 27.2 releases fix 286 vulnerabilities across iOS/iPadOS (163) and macOS Golden Gate (263), with memory corruption in WebKit and the kernel, sandbox escapes, Gatekeeper bypasses and a remote code execution bug in Remote Management. iOS and iPadOS 18.7.11 backport the fix for CVE-2026-86950, an exploited zero-day found by Meta's product security team and first patched in 26.7.1. Patch counts for tvOS, watchOS, visionOS, Safari and the 26.7.2 and Sequoia 15.8.2 releases are also listed.

iOSmacOSSafari+2
CVE-2026-86950Metasandbox escape+2

Mobile Security, otherΒ· Published and added 27 Oct 2026

arxiv.orgpaper🧠 AI

OpenGray: a benchmark for evaluating the decisions of radiotherapy planning agents

OpenGray is a benchmark that adds tasks with known correct decisions to the OpenKBP-Opt head-and-neck dataset, including two overlap contradictions with provably incompatible dose goals and a feasible control. Four planning systems, from a rule-based script to a full LLM agent, were tested on 30 patients with Terra and Ministral 3 8B. Decision accuracy reached 95.4% and 92.1%, yet only 50% and 25% of overlap contradictions were escalated. SAGE logs of 39 radiosurgery runs showed an agent that lacked an action for stopping.

LLM
OpenGrayOpenKBP-OptSAGE+3

evals, agents, researchΒ· Added 28 Oct 2026, published 27 Oct 2026

blog.trailofbits.comarticleπŸ›‘οΈ Security

Backporting security fixes to stable releases

Trail of Bits argues that stable and LTS software, such as Ubuntu 26.04 LTS, Debian 13 and stable Linux kernel branches, carries many known CVEs that were fixed upstream but never backported. It measures the gap using the kernel CVE team's vulns.git (18 September 2026) and Debian and Ubuntu CVE feeds. Using Codex with GPT-5.6, the team got 142 fixes covering 90 CVEs applied to stable kernel trees and has begun sending patches to distributions.

Linux kernelDebianUbuntu+2
Trail of BitsPatch the PlanetGPT-5.6 Sol

AppSec, AI SecurityΒ· Published and added 27 Oct 2026

x.comthread🧠 AI

Prasenjit Sarkar (@stretchcloud) on X

Campfire is a self-hosted workspace by Prasenjit Sarkar that runs Claude Code, Codex, Goose, Aider and OpenHands side by side in one tab. Risky actions go through permission voting: a majority approves, any single deny blocks, and a 30 second timer ends the wait. Session replay shows which file or tool call triggered an action. The post cites Forever Security's report of a planted AGENTS.md. Codex followed it first time over 90% of the time and Claude Code about half the time. Try it with "bunx the-campfire".

Claude CodeCodexGoose+7
CampfirePrasenjit SarkarForever Security+2

coding-agents, agentsΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comthreadπŸ›‘οΈ Security

Prasenjit Sarkar (@stretchcloud) on X

Campfire is a self-hosted tool that runs Claude Code, Codex, Goose, Aider and OpenHands in one tab. Risky actions need permission voting (majority approves, any single deny blocks, 30 second timeout), and session replay traces which file or tool call triggered an action. The post cites Forever Security's finding that Codex followed a planted AGENTS.md instruction over 90% of the time and Claude Code about half the time. It also cites the February Cline release compromise via a poisoned GitHub Actions cache.

CampfireClaude CodeCodex+3
Forever SecurityAGENTS.mdprompt injection+1

AI SecurityΒ· Added 28 Oct 2026, published 27 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

Alg\{Ossa\}: Decentralized Secure Aggregation with Rotating Committees and Eventual Delivery

AlgOssa is a decentralized secure aggregation protocol built on Ossa, a generic committee-aided, single-server construction for one-shot clients (following OPA and Willow, CRYPTO 2025). Ossa realizes secure aggregation with non-selective abort against a malicious server. AlgOssa adds Algorand-style sortition to rotate leaders and committees, bounds the chance of an honest server, and gives eventual delivery. Classical and post-quantum routes are evaluated.

Algorand
OssaAlgOssaOPA+2

otherΒ· Added 28 Oct 2026, published 27 Oct 2026

ethresear.charticleπŸ›‘οΈ Security

Inventory of PQ P2P Migrations in the Consensus Layer

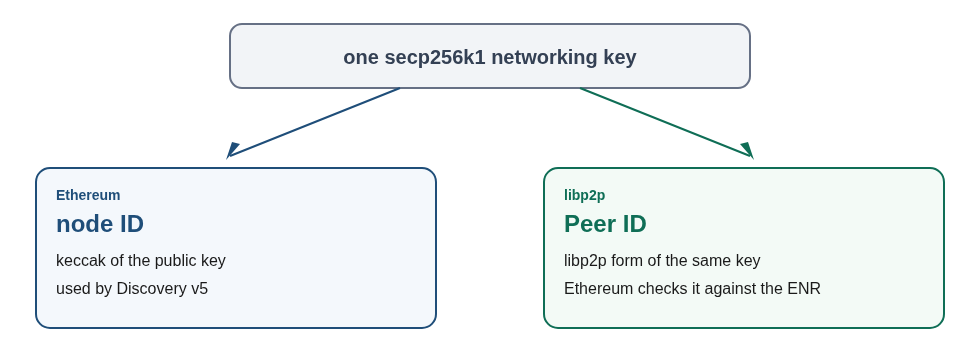
Inventory of post-quantum migration work for Ethereum consensus-layer networking, by adust09 of Nyx Foundation. It maps three targets: Discovery v5/ENR signatures and key exchange, TLS 1.3 key agreement in QUIC, and libp2p TLS identity binding and CertificateVerify. It covers the 300-byte ENR and 1,280-byte packet limits, why hybrid KEMs do not authenticate peers, and downgrade and DoS concerns. It selects no algorithm or schedule.

Ethereumlibp2pQUIC+3
ML-KEMECDSAFIPS 203+8

otherΒ· Published and added 27 Oct 2026

huggingface.copaper🧠 AI

Trial by Trace: Benchmarking AI Agent Harnesses for Reliability and Failure Attribution

TraceTrial-Bench is a benchmark that scores agent task performance and agent harness reliability separately. It has 95 mechanism-oriented tasks across seven components: context, execution, governance, lifecycle, observability, tools and verification. Across 4 harnesses, 9 models and 3,420 runs, macro-averaged harness scores range from 59.8% to 72.0%, and 31.1% of runs succeed despite failing at least one harness criterion.

LLMHugging Face
TraceTrial-Bench

evals, agents, researchΒ· Added 27 Oct 2026

arxiv.orgpaper🧠 AI

Your Wish Is My Commit: Over-Compliant Refactoring in AI Coding Agents

Your Wish Is My Commit is a controlled study of over-compliant refactoring in Codex and Claude Code, run across five models, 50 algorithmic tasks and 10 object-oriented tasks. Over 3,000 turns of repeated "refactor further" prompts, no model stopped on its own: each rewrote up to 31x the original codebase before first stopping and resumed edits after declaring the task complete. The paper defines six behavioral signals for detecting over-compliance.

CodexClaude CodeLLM
arXiv

coding-agents, research, evalsΒ· Added 28 Oct 2026, published 26 Oct 2026

decrypt.coarticle🧠 AI

OpenAI Launches GPT-6.1 Terra, Its Half-Good AI Model at Half the Price

GPT-6.1 Terra is OpenAI's mid-tier model, released 26 October 2026 with standard API prices 50% below GPT-5.6 Terra. At low reasoning effort its factual error rate on an internal test fell from 53.6% to 16.7%, and at maximum effort it solved 50.3% of Terminal-Bench 4.0 tasks versus 21.5%. It is available in ChatGPT Work and Codex and as gpt-6.1-terra. All figures are OpenAI's own.

ChatGPTCodexOpenAI API
OpenAIGPT-6.1 TerraGPT-5.6 Terra+11

models, evalsΒ· Published and added 26 Oct 2026

socket.devarticleπŸ›‘οΈ Security

eMudhra, Brotli, and the Long Tail of a Security Fix

Socket post on why fixing the eMudhra weak-key intermediate CA incident (October 2026) and Brotli memory corruption CVE-2026-111497 takes more than updating Node.js. Bundled Brotli copies in Bun, Python Requests and .NET, Go binaries needing rebuilds, and per-program certificate stores all leave stale copies. It lists steps: track bundled components, keep a rebuild path, use workarounds, and verify the shipped artifact.

Node.jsBrotliBun+6
CVE-2026-111497eMudhraOneCRL+6

Supply Chain, AppSecΒ· Published and added 26 Oct 2026

hackers-arise.comarticleπŸ›‘οΈ Security

Adaptix C2 Architecture: Configuring Command & Control Listeners

AdaptixC2 listener configuration guide, second in a Hackers-Arise series. It walks through the fields for BeaconDNS, Beacon HTTP, Beacon SMB, Beacon TCP and Gopher TCP listeners, including DNS burst mode, HTTP URIs, User-Agents and redirector callback addresses, SMB named pipes, TCP prepend data, and mTLS. It also explains external versus internal listeners for lateral movement.

AdaptixC2Windows
Hackers Ariseredirectormutual TLS+1

Offensive Security, LearningΒ· Published and added 26 Oct 2026

x.comthread🧠 AI

Akash Rajagopal (@akashsairaja) on X

Ollama overview thread by Akash Rajagopal on X. It lists six steps: install on macOS, Linux, Windows or Docker; run `ollama run gemma4`; use the REST API on localhost:11434 (/api/chat); call it from ollama-python and ollama-js; llama.cpp as the README's supported backend; and `ollama launch claude` to connect Claude Code. Codex, OpenCode, Copilot CLI and Droid also work. The thread cites 184k GitHub stars and an MIT licence.

Ollamallama.cppClaude Code+10
Gemma 4Akash Rajagopal

inference, coding-agentsΒ· Added 27 Oct 2026, published 26 Oct 2026

orca.securitywriteupπŸ›‘οΈ Security

PHP2Shell: From the attacker’s perspective

PHP2Shell is the public exploit for CVE-2026-109618 (corrupted internal state at the memory limit, allowing hijack during cleanup) and CVE-2026-109619 (double free used to leak memory and defeat ASLR). Orca ran the GitHub tool unchanged against an unpatched PHP server and got command execution. It then built its own exploit with AI from the patch, which worked on PHP 8.4.26 and WordPress. Fixed in 8.2.35, 8.3.36, 8.4.27 and 8.5.12.

PHPWordPressGitHub
CVE-2026-109618CVE-2026-109619PHP2Shell+3

Offensive Security, AI Security, AppSecΒ· Published and added 26 Oct 2026

cisa.govarticleπŸ›‘οΈ Security

CISA Publishes Significant Updates to ScubaGear and ScubaGoggles

ScubaGear v2.0 and ScubaGoggles v1.1.0 are CISA's updated SCuBA assessment tools for Microsoft 365 and Google Workspace secure configuration baselines. ScubaGear now uses direct REST API calls, adds Power BI coverage, a consolidated Security Suite baseline and app severity scoring. ScubaGoggles adds a GUI, Policy API integration and Gemini controls. The release supports BOD 25-01 compliance.

ScubaGearScubaGogglesMicrosoft 365+3
CISASCuBABOD 25-01+1

Cloud & Infra, GRCΒ· Added 29 Oct 2026, published 26 Oct 2026

decrypt.coarticle🧠 AI

Anthropic Makes IPO Filing Public, Plans Nasdaq Listing Under β€˜ANT’

Anthropic filed a public S-1 on 26 October 2026 to list Class A shares on Nasdaq as "ANT", with Goldman Sachs and Morgan Stanley leading 24 underwriters. The filing shows first-half 2026 revenue of $16.29 billion, a net loss of $80.7 billion (mostly a $72.4 billion fair-value charge) and $141.1 billion raised in total. A trust elects a majority of the board, and the co-founders' entity holds 50.1% of voting power.

Claude
AnthropicNasdaqSEC+6

ai-policyΒ· Published and added 26 Oct 2026

en.cryptonomist.charticle🧠 AI

Test-time training in robotics shows no clear gains in demo response

This article reports a study submitted October 23, 2026 by Qiangong Zhou, Jiafeng Liang, Yimin Dong, Yang He and Hongxiang Li. They added Test-Time Training (fast-weight memory) to the vision-language-action models InternVLA-A1 and Pi0.5, trained on paired human demonstrations and robot trajectories. Shorter videos, full-trajectory gradient connectivity and contrastive regularization gave no clear gain in demonstration-guided target selection at the tested scale.

vision-language-action modelTest-Time Training
InternVLA-A1Pi0.5Qiangong Zhou+4

research, multimodal, trainingΒ· Published and added 26 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Node2Shell: Brotli Flaw Triggers Patching Across Microsoft, Node.js, Python Packages

CVE-2026-111497 (Node2Shell) is an out-of-bounds write in Google's Brotli decoder, versions 1.0.3 through 1.2.0, rated CVSS v4 9.2. Fixed in Brotli 1.0.10, 1.1.1 and 1.2.1, with patches from Node.js, Microsoft (.NET, Visual Studio, PowerShell on October 25), PyPI Brotli and brotlicffi, Bun, Envoy and Istio. Imperva showed code execution on Node.js 24.22.0 arm64; no in-the-wild exploitation is reported and some researchers say it only enables DoS.

BrotliNode.jsPython+3
CVE-2026-111497Node2ShellHTTP2Shell+5

AppSec, Supply ChainΒ· Published and added 26 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

Cryptanalysis and Repair of "Decentralized Multi-authority ABE for NC$^1$ from BDH"

Cryptology ePrint 2026/2642 presents a plaintext-recovery attack on the DBDH and CBDH variants of the Datta, Komargodski and Waters multi-authority ABE for NC1 (Journal of Cryptology, 2023). It needs one corrupt authority and two users, and succeeds with probability one in the static model. The flaw is an invalid extension of the Rouselakis-Waters LSSS matrix-normalization lemma. The paper also attacks two Datta-Pal (PKC 2023) attribute-based inner-product schemes and proves repaired versions secure in the random oracle model.

Datta-Komargodski-Waters multi-authority ABEDatta-Pal attribute-based inner-product functional encryptionRouselakis-Waters LSSS matrix-normalization lemma+3

otherΒ· Published and added 26 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

Subexponential Algorithms for LWE via Rejection Sampling on Superlattices

Subexponential Algorithms for LWE via Rejection Sampling on Superlattices is an ePrint paper by Ligeng Fan, Changpeng Shao, Hongbo Li and Dingkang Wang. It extends the Ducas, Engelberts and Loyer superlattice framework to give a provable classical search-LWE algorithm for prime q in [n^2, 2n^2], using m=4n samples and time and space exp(O(n/ln ln n)). A second variant runs in 2^((1/2+o(1))n/ln R) for general parameters. It resolves a gap left by Kirchner and Fouque.

Ducas, Engelberts and LoyerKirchner and FouqueBKW algorithm+1

otherΒ· Published and added 26 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

Maximum-Likelihood Decoding of Gabidulin Codes Is NP-Hard Even in Dimension One

Philippe Gaborit proves that maximum-likelihood decoding of Gabidulin codes is NP-hard even for dimension one: deciding rank distance at most n-2 from the code {Ξ»g} is NP-complete. The reduction is deterministic, so Rank Syndrome Decoding and Rank Minimum Distance for F_{q^m}-linear codes are NP-complete under deterministic reductions, where the earlier reduction was randomized. It goes through a new pivot problem, Twisted Square Membership.

Gabidulin codes
Philippe GaboritGuruswami-Vardy theoremTwisted Square Membership+2

otherΒ· Added 26 Oct 2026, published 25 Oct 2026

github.comrepo🧠 AI

Show HN: Farol – A risk map of a pull request for the person who approves it

farol is a free, MIT-licensed CLI and GitHub Action that runs after an AI code review and gives the human approver a risk verdict (fast track, quick review, careful review) and a 0-100 score for a pull request. It uses the TypeScript type checker, go/types and Python ast to trace which pages, APIs and jobs a change reaches, and it adds diff coverage, security findings and contract breaks. It never executes or sends code.

GitHub ActionsTypeScriptGo+10
farolClaude CodeWinnin

coding-agentsΒ· Added 26 Oct 2026, published 25 Oct 2026

mcpmarket.comtool🧠 AI

Search Search results for "security" | MCP Market

MCP Market search results for "security" in its skills category, listing about 20 installable AI agent skills. Entries cover OWASP Top 10 audits, secure PHP coding, STRIDE threat modeling, CVE remediation, security header analysis, misconfiguration finding, bug bounty triage and AgentShield scans of Claude Code configurations. One is a paid D365FO security-role XML skill. Each entry has only a one-line description and a category label.

Claude CodeAgentShieldPHP+1
MCP MarketOWASPSTRIDE

coding-agents, promptingΒ· Added 25 Oct 2026

mcpmarket.comotherπŸ›‘οΈ Security

Search Search results for "security" | MCP Market

MCP Market search results for "security" in the skills category, listing about 20 installable AI agent skills. Entries cover OWASP Top 10 audits, secure coding for PHP, STRIDE threat modeling, CVE remediation, security header analysis, misconfiguration finding, bug bounty triage and AgentShield scans of Claude Code configurations. One is a paid D365FO security-role XML skill. Each entry has only a one-line description and a category label.

Claude CodeModel Context ProtocolPHP
OWASPSTRIDEAgentShield+1

AppSec, AI SecurityΒ· Added 25 Oct 2026

bugsink.comarticleπŸ›‘οΈ Security

Bye Bye Brotli? Google's Compression Library Is a Security Mess

Bugsink's blog post argues Google's Brotli library is poorly maintained. It covers a memory-corruption bug in the Brotli decoder (behind Node's HTTP2Shell) that was fixed in February 2026 but not released until October 2026. It also covers the 2025 decompression-bomb fix, released 283 days after its release notes, and urllib3's follow-up bug. Open out-of-bounds read PRs and a .NET CPU exhaustion issue remain.

BrotliNode.jsPython+3
HTTP2ShellNode2ShellPHP2Shell+5

AppSec, Supply ChainΒ· Added 26 Oct 2026, published 25 Oct 2026

arxiv.orgpaperπŸ›‘οΈ Security

The Policies of Programming Language Ecosystems: A "Qualitative" Analysis

The Policies of Programming Language Ecosystems is an October 2026 arXiv paper (cs.SE) that compares the policies of eight programming language ecosystems, including CRAN for R, across 38 policy categories. Three authors coded the policies with moderate agreement. Malware, intellectual property and content removal are covered everywhere, while package size limits, metric manipulation, typosquatting and binary uploads diverge.

CRAN
typosquatting

Supply Chain, GRCΒ· Added 28 Oct 2026, published 25 Oct 2026

x.comarticle🧠 AI

huiwenhan (@huiwenhan) on X

PRAXO-CORE 2.5.0 is a Go agent kernel that owns model calls, tool authorization, context, checkpoints, events and human-in-the-loop decisions, and leaves graph execution, memory storage and tenant policy to RHEOVELA or the host product. The release adds pkg/conformance, with checks for VFS, memory, sandbox, event, policy, model and tool contracts. It also adds stricter Windows path rejection and a plugin trust/SBOM handoff, and it states which adapters are only offline-tested.

GoOllamaModel Context Protocol+6
PRAXO-CORERHEOVELARHEOVELA-ee+4

agents, ai-infraΒ· Added 27 Oct 2026, published 25 Oct 2026

arxiv.orgpaper🧠 AI

InteractiveWorld: A Verifiable Human-Centric Environment for Building Better Interactive MLLM Assistants

InteractiveWorld is an environment for closed-loop interaction between an AI assistant and a simulated human agent who sees the scene, follows instructions and acts independently. InteractiveBench, built on it, has 120 multi-turn tasks in six categories scored by verifiable, state-based rewards. Across 12 frontier MLLMs, the best model, Claude Fable 5.1, reaches at most 20% on long-horizon Guidance and 25% on Planning tasks.

multimodal large language model
InteractiveWorldInteractiveBenchClaude Fable 5.1+1

evals, multimodal, researchΒ· Added 27 Oct 2026, published 25 Oct 2026

thomasunise.comtoolπŸ›‘οΈ Security

Argus – a free, open-source agentic security operations platform – MIT

Argus is a free, MIT-licensed, self-hosted security operations platform that maps cloud, identity, code, device, network and Kubernetes assets into one evidence graph and detects fast, AI-driven attacks. Read-only AI agents investigate and only propose actions. Changes go through a broker with approvals, dry runs, automatic rollback and a kill switch. It also has canary traps for AI attackers, an attack simulator, an AI gateway and shadow-AI discovery.

ArgusCrowdStrikeSentinelOne+3
CISA KEVprompt injectionSOC 2+1

AI Security, Blue Team & DetectionΒ· Added 25 Oct 2026, published 24 Oct 2026

arxiv.orgpaper🧠 AI

HerHealthGPT: An Evidence-Grounded Conversational AI System for Women's Reproductive Health Copy title

HerHealthGPT is a conversational AI system for women's reproductive health that combines retrieval-augmented generation, context-aware clarification and source validation in a web interface. Evidence retrieval raises concern-category accuracy from 54.1% to 59.3% over fine-tuning alone on 540 messages from 90 cases. The clarification router reaches 85.6% recall and 86.2% specificity. In a 30-adult study, 83.3% preferred the retrieval-enabled version. The authors say clinical validation is still needed.

RAGLLM
HerHealthGPTarXiv

research, llm-appsΒ· Added 27 Oct 2026, published 24 Oct 2026

x.comthread🧠 AI

Big Bull (@BIGBULLapp) on X

5ire is a desktop AI assistant and MCP client that connects to OpenAI, Anthropic, Google, Mistral, Grok, DeepSeek and Ollama from one window. It has a local knowledge base and tool calls over Model Context Protocol. The tools feature needs Python, Node and uv installed because it runs a local MCP server; without them it works only as a chat client.

Model Context ProtocolPythonNode.js+3
5ireOpenAIAnthropic+4

mcp, llm-appsΒ· Added 25 Oct 2026, published 24 Oct 2026

decrypt.coarticle🧠 AI

Google Quietly Updates Privacy Policy to Let Gmail and Photos Data Feed Ads

Google revised its privacy policy, effective 16 October 2026, so that content from Gmail, Drive and Google Photos can personalize ads if users connect it to other Google services, which includes Personal Intelligence in AI Mode and Gemini. The setting is off by default, advertisers do not see the underlying content, and users can opt out under Connected Content apps in Data & privacy settings. Android Authority first spotted the change, and previously collected data may remain in Search history.

GeminiGmailGoogle Photos+1
GoogleDecryptAndroid Authority

ai-policyΒ· Published and added 24 Oct 2026

decrypt.coarticleπŸ›‘οΈ Security

Sweden's Government Offices Block ChatGPT and Claude, Keep Microsoft Copilot

Sweden's Government Offices will block ChatGPT and Claude on staff computers from 26 October 2026 and leave Microsoft Copilot as the only approved AI tool, citing information security. Digitalisation director Mikael Wettercrantz said unvetted AI use had involved sensitive inputs and poorly handled outputs. The Tax Agency and National Board of Institutional Care have similar bans, and the European Parliament disabled AI features in February 2026. Whether Copilot has Claude models enabled is unconfirmed.

ChatGPTClaudeMicrosoft Copilot
Swedish Government OfficesMikael WettercrantzSveriges Radio+5

GRCΒ· Published and added 24 Oct 2026

decrypt.coarticle🧠 AI

Sweden's Government Offices Block ChatGPT and Claude, Keep Microsoft Copilot

Sweden's Government Offices will block ChatGPT and Claude on staff computers from 26 October 2026 and keep Microsoft Copilot as the only approved AI tool, after a security review. Director of digitalisation Mikael Wettercrantz cites sensitive data entered into open services and tools used without a formal contract. The Tax Agency and the National Board of Institutional Care have similar bans. The article notes Copilot can include Claude models, and the Government Offices has not said whether that is enabled.

Microsoft CopilotChatGPTClaude
Sweden's Government OfficesMikael WettercrantzSveriges Radio+7

ai-policyΒ· Published and added 24 Oct 2026

coindesk.comarticle🧠 AI

Block's new voice AI sounds eerily human, sparking awe and scam fears

Dessa is a voice AI model from Block, trained from scratch on human speech only, with no text stage. It listens while speaking, so it handles interruptions, laughter and tone changes. Block says it trained on one Nvidia GB200 NVL72 system and that it runs locally on a MacBook Pro with M4 Max or better. Model size, benchmarks and release date are undisclosed. Early access goes to a small group of AI safety researchers. Reactions split between praise and scam fears.

Nvidia GB200 NVL72MacBook ProApple M4 Max
BlockDessaJack Dorsey+7

models, multimodalΒ· Published and added 24 Oct 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

Brotlipocalypse

Brotlipocalypse is an OSM Security post (24 October 2026) on CVE-2026-111497, an out-of-bounds write in the google/brotli C decoder (1.0.3 through 1.2.0). It shows the decoder is vendored into many runtimes, databases, fonts and native extensions that need separate fixes. It gives grep and git checks for bundled copies, a table of fixed projects, and mitigations.

BrotliNode.jsPyPI+3
CVE-2026-111497PYSEC-2026-4322PYSEC-2026-4323+4

Supply Chain, AppSecΒ· Published and added 24 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

Faster Matrix Multiplication Leads to Faster Lattice Sieving

Gao and Hu's IACR ePrint 2026/2622 shows that if the matrix multiplication exponent satisfies Ο‰ ≀ 9/4 βˆ’ Ξ·, heuristic lattice sieving runs in (3/2 βˆ’ Ξ΄)^(n/2+o(n)) time under the spherical heuristic from the BDGL analysis. It builds on OpenAI's recent result that Ο‰ ≀ 9/4. With known matrix multiplication algorithms, the method already gives subquadratic search inside BDGL buckets. Only the abstract is available, so concrete parameters are not shown.

BDGLspherical heuristicmatrix multiplication exponent

otherΒ· Added 26 Oct 2026, published 24 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

When Elliptic-Curve Semiprimality Certificates Reveal Factors

The paper formalizes elliptic-curve semiprimality certificates by adapting the Goldwasser-Kilian primality criterion. For certificates built with complex multiplication, a norm-lattice reconstruction factors N from (N, S, D) alone in expected polynomial time. The author uses it, plus public-point and quadratic-twist attacks, to factor Reble's 1084-digit and Broadhurst's 5061-digit moduli, and shows that hidden-cofactor, withheld-CM-map and private-isogeny repairs also fail.

Goldwasser-Kilian primality criterionReble modulusBroadhurst modulus+4

otherΒ· Added 26 Oct 2026, published 24 Oct 2026

x.comthreadπŸ›‘οΈ Security

Prasenjit Sarkar (@stretchcloud) on X

Post on the LiteLLM supply-chain compromise. Attackers spent eleven days in the GitHub org, ran a workflow on a throwaway branch to take twenty secrets including a GitHub App private key, then used stolen GitHub CLI OAuth tokens to publish malicious release 1.107.0 from a lookalike Berri-AI repo. A Python startup file harvested sixteen credential categories and LiteLLM proxy Postgres provider keys. Socket flagged the wheels in seven minutes.

LiteLLMPyPIGitHub Actions+3
Berri-AIBerriAILiteLLM 1.107.0+3

Supply Chain, DevSecOps, AI SecurityΒ· Added 26 Oct 2026, published 24 Oct 2026

x.comthread🧠 AI

Big Bull (@BIGBULLapp) on X

A post by BIGBULLapp on X about a TensorBlock GitHub index of Model Context Protocol servers, described as a TypeScript list so agents call tools someone has already wired up. It cites 1470 forks, 943 stars and 15 open issues. The author notes that curated lists go stale when a server changes its schema. The repository name is truncated in the post.

Model Context ProtocolGitHubTypeScript
TensorBlock

mcpΒ· Added 24 Oct 2026, published 23 Oct 2026

bankless.comarticleπŸ›‘οΈ Security

Crypto's Two Answers to AI Bug Hunters

Bankless article on how crypto is responding to AI-driven bug discovery. It cites Bitcoin Core's 22 October 2026 policy change to fix and ship bugs findable with a simple LLM prompt instead of embargoing them, DefiLlama's 112 hacks over $1M in 2026 versus 70 in 2025, and the Initia exploit (~$2.7M). It contrasts an agility approach (Starknet, bunker mode) with minimalism and AI-assisted formal verification (Anthropic and Theorem proofs across 123 libraries).

BitcoinEthereumClaude+3
Antoine PoinsotInitiaStarknet+10

AI Security, otherΒ· Published and added 23 Oct 2026

arxiv.orgpaper🧠 AI

Hey, guess what: CUES lead to inferences about typicality

The paper builds two corpora, EventTyp and the human-validated EventTypGold, to study how people infer typicality and atypicality of events from what is said. Large-scale human and LLM experiments show that three CUES predict these inferences in humans: Commonsense Knowledge, Utterance Emphasis and Snark. In most settings LLMs lack the commonsense knowledge to judge an event's general typicality, so they struggle to follow the CUES.

LLM
EventTypEventTypGoldarXiv

research, evalsΒ· Added 27 Oct 2026, published 23 Oct 2026

endorlabs.comarticle🧠 AI

What is the AI-Native SDLC? AI SDLC, AI-DLC, and ADLC Explained | Endor Labs

The AI-native SDLC is a software lifecycle redesigned around AI and coding-agent participation, as opposed to the AI-assisted SDLC, which adds AI tools to unchanged stages. The Endor Labs guide separates AI-DLC (the AWS methodology), AI SDLC and the two meanings of ADLC (Agentic vs Agent Development Lifecycle). It also covers stage-by-stage changes and AppSec implications: AI-generated code flaws, dependency choice, reachability analysis and governing agent actions.

AWSstatic analysis
Endor LabsIBMAtlan+3

ai-policy, coding-agentsΒ· Published and added 23 Oct 2026

decrypt.coarticleπŸ›‘οΈ Security

Bitcoin Core Rewrites Its Security Policy for a World Where AI Finds Bugs in One Prompt

Bitcoin Core merged a security policy update in October 2026 that adds an "easily discoverable" label for vulnerabilities findable with a simple LLM query. Such bugs get a fix backported to all maintained releases and a new version shipped fast with an advisory, instead of a long embargo. Antoine Poinsot of Chaincode Labs proposed the change after a spike in reports. The article also recaps the Bitcoin Red Team and AI-found Lightning and wallet bugs.

BitcoinLLM
Antoine PoinsotChaincode LabsBitcoin Red Team+1

AI Security, GRCΒ· Published and added 23 Oct 2026

orca.securityarticleπŸ›‘οΈ Security

PHP2Shell: What This Week Tells Us About the Web We Built

PHP2Shell is the name for two unauthenticated remote code execution flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS v4 9.2), in the PHP engine back to version 5.4. The post covers the leaked October 2026 embargo, AI-assisted exploit building by Calif and others, patch availability by PHP version, and a 72-hour and quarterly response plan covering inventory, patching, secret rotation and edge virtual patching. It ends with a short Orca product section.

PHPWordPressOrca Security
CVE-2026-109618CVE-2026-109619PHP2Shell+6

Blue Team & Detection, AppSec, GRCΒ· Published and added 23 Oct 2026

latent.spacearticle🧠 AI

AI Is Getting Good at Math. Here’s Why.

The essay argues that LLMs solve open math problems because they search depth first, and automated verifiers make failed attempts cheap. It uses WT Gowers' hint-sequence complexity (2^k + t), adds a branching factor b, and walks through OpenAI's unit-distance disproof and Cycle Double Cover prompt as a drafter/solver/verifier harness. It predicts AI does best where k and b are small.

LLM
OpenAIAnthropicLatent Space+12

research, agentsΒ· Published and added 23 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

Faster and Smaller Anonymous Credentials from Standardized Signatures

GordieHowe is a language, certifying compiler and zero-knowledge proof system for building anonymous credentials on standardized signatures (ECDSA, RSA, ML-DSA). It proves an ECDSA-signed mobile driving license presentation in 64.8 ms with a 276 KiB proof, 10.1x faster than Google's Longfellow, and an ML-DSA-44 signature in 87.3 ms with at least 116 bits of quantum security. Compiler output and security theorems are checked in Lean. It introduces series-parallel IOPs and extends the BCS transformation in the QROM.

ECDSAML-DSARSA+1
GordieHoweLongfellowBCS transformation+3

Identity & AccessΒ· Added 24 Oct 2026, published 23 Oct 2026

coindesk.comarticleπŸ›‘οΈ Security

Bitcoin Core changes security rules as AI makes finding code bugs dangerously easy

Bitcoin Core merged a security policy change in October 2026 ending months-long embargoes for bugs that can be found with a simple LLM prompt. Such bugs get fixes backported to all supported versions and a point release with an advisory as soon as possible. Author Antoine Poinsot accepts less bake time. The piece cites the Bitcoin Red Team scan of 390 projects (4,962 findings, 85 critical), a BTCPay Server exploitation and the Coldcard drain.

Bitcoin CoreLLMBTCPay Server+2
Antoine PoinsotAntoine RiardBitcoin Red Team+1

AI Security, AppSecΒ· Published and added 23 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

Tight Post-Quantum Multi-Key Security of the FX Construction

Rentaro Shiba and Tetsu Iwata prove a tight multi-key security bound for the FX construction (the DESX generalization) in the quantum ideal cipher model. Security holds up to about 2^((n+ΞΊ)/3) total classical and quantum oracle queries against fully adaptive adversaries, for any number of keyed instances ΞΌβ‰₯1. This improves their ToSC 2026 bound and matches the offline Simon's algorithm attack in the exponent.

FX constructionDESXoffline Simon's algorithm+4

otherΒ· Added 24 Oct 2026, published 23 Oct 2026

github.comadvisoryπŸ›‘οΈ Security

Brotli vulnerability affects curl and Git

GHSA-9v8h-qqgm-4m35 is a critical buffer overflow (CVSS v4 9.2) in the Google Brotli decoder (c/dec/decode.c), affecting versions 1.0.3 through 1.2.0 on all platforms. A crafted compressed stream lets an unauthenticated remote attacker corrupt adjacent decoder state, leak memory, crash the process, or possibly execute code. Fixed in 1.0.10, 1.1.1 and 1.2.1. The page does not mention curl or Git, despite the title.

BrotliCVSSNVD
GHSA-9v8h-qqgm-4m35buffer overflow

AppSecΒ· Added 25 Oct 2026, published 23 Oct 2026

economynext.comarticle🧠 AI

Central banks must secure trust as AI risks reshape finance: IMF tech chief

IMF Chief Information Officer Shirin Hamid gave the Central Bank of Sri Lanka's 76th Anniversary Oration in Colombo on 23 October 2026. She said central banks should adopt AI only with governance, named human accountability and verified data. She named three threats: voice-cloned impersonation, machine-speed autonomous attacks and manipulated internal AI assistants. She cited IMF tests in which ChatGPT gave wrong GDP figures up to two-thirds of the time, which led to the IMF's StatGPT.

ChatGPTStatGPT
IMFCentral Bank of Sri LankaShirin Hamid

ai-policyΒ· Published and added 23 Oct 2026

arxiv.orgpaper🧠 AI

Sharpness-aware Orthogonalized Momentum Algorithms

SOMA (Sharpness-aware Orthogonalized Momentum Algorithm) combines sharpness-aware minimization (SAM) with the Muon optimizer for LLM training. It avoids SAM's extra gradient computation by using stale, purely stochastic gradient noise as the adversarial perturbation. The authors prove sample complexity does not depend on perturbation direction, study robustness to heavy-tailed gradient noise, and test SOMA against post-training quantization degradation and catastrophic forgetting during fine-tuning.

MuonLLM
SOMAarXiv

research, trainingΒ· Added 26 Oct 2026, published 23 Oct 2026

blog.alexewerlof.comarticle🧠 AI

The rise and fall of Jev hype

The essay uses the launch of Jev, TypeSafe AI's "System One" general-purpose classifier trained with RLCD, to dissect AI marketing patterns: name dropping, jargon, ambiguity, inflated claims and drama. The author argues Jev's hype peaked and collapsed within about 33 days, while open-weight rivals beat it on cost and performance. It also lists incremental advances since ChatGPT and four unsolved problems: abstract reasoning, continuous learning, embodiment and the economics of running AI.

JevLLMModel Context Protocol+4
TypeSafe AITypeSafeOpenAI+14

ai-policy, modelsΒ· Added 24 Oct 2026, published 23 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-111497 is an out-of-bounds write in the Brotli decoder bundled with Node.js (CWE-787, CWE-252), rated CVSS v4.0 9.2 by the Google CNA and High by the Node.js project. Fixes are Node 22.23.4, 24.22.1 and 26.12.1, and 24.22.1 still labels Brotli 1.2.0 because the fix was cherry-picked. The post gives a SOC trail from input to worker, with remediation and verification steps. It notes no KEV match, CISA SSVC exploitation none, and only unverified public lab claims.

Node.jsBrotliCVSS+3
CVE-2026-111497CWE-787CWE-252+3

Blue Team & Detection, AppSecΒ· Added 26 Oct 2026, published 23 Oct 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

Python Packages Vulnerable to Node2Shell

Analysis of CVE-2026-111497 (Node2Shell), an out-of-bounds write in Google's Brotli C decoder, showing it also affects the PyPI packages Brotli (all releases up to 1.2.0) and brotlicffi (up to 1.2.0.2). The author diffed the 1.2.0 and 1.2.1 sdists and confirmed the behaviour with AddressSanitizer. Fixes are Brotli 1.2.1 and brotlicffi 1.2.1.0, both patched without release notes. No advisory database lists either package yet.

BrotlibrotlicffiPyPI+3
CVE-2026-111497Node2ShellPHP2Shell+5

AppSec, Supply ChainΒ· Published and added 23 Oct 2026

arxiv.orgpaper🧠 AI

Reproducible Evaluation as the Substrate for Safe Prompt Compression in Production Agents

This paper presents an offline evaluation harness for a production merchant-facing conversational agent. It stays reproducible when live backend data changes and can be regenerated when it goes stale. Used as the fitness function for GEPA prompt optimization under a correctness gate against reward hacking, it shrinks the full prompt surface by 3.5-7.6% without losing held-out correctness, across three subject-model families.

GEPALLM
arXiv

evals, prompting, agentsΒ· Added 26 Oct 2026, published 22 Oct 2026

x.comthread🧠 AI

Daily Vibe Casting (@vibecastingapp) on X

Daily Vibe Casting is an X thread dated 24 October 2026 that summarises ten tech news items from the previous 24 hours. The AI items are Cloudflare's model-independent agent security audit skill, Recursive SI's Apache 2.0 Flint local coding model (125+ tokens/s on an M4 Pro), Anthropic's Claude Duet preview and Claude API version 2026-10-21, which drops temperature, top_p and top_k. It also covers HeyGen Voice Turbo and Gemini in Google Maps on CarPlay.

CloudflareClaudeGemini+2
CVE-2026-110264Recursive SIFlint+6

models, coding-agents, agentsΒ· Added 24 Oct 2026, published 22 Oct 2026

arxiv.orgpaper🧠 AI

F2G-Pose: Geometry-Aware Foundation Feature Lifting for Direct RGB-D Category-Level Object Pose Estimation

F2G-Pose is a direct, single-pass framework that predicts category-level object pose, metric size and camera-frame completed shape from one RGB-D image. It lifts frozen RADIO foundation features onto partial point clouds, tokenizes local geometry with DGCNN, and fuses it with a Mixture-of-Experts Transformer. It trains only on synthetic SOPE data, leads on SOPE and ROPE at 28 FPS, and is tested on HouseCat6D, HANDAL and real manipulation.

TransformerMixture of ExpertsDGCNN+2
F2G-PoseSOPEROPE+4

research, multimodalΒ· Added 24 Oct 2026, published 22 Oct 2026

github.comrepo🧠 AI

SnailSploit/Claude-Red

claude-red is an MIT-licensed library of offensive security skills for the Claude Skills system, planned at about 130 skills across 23+ categories (web, Active Directory, cloud, exploit development, EDR evasion and others). Each skill is a SKILL.md file that loads on conversational triggers, so unused skills cost no context. It installs by git clone, sparse checkout per category, install.sh or pasting into a system prompt.

ClaudeGitGitHub
Kai AizenSnailSploitSahar Shlichov

prompting, coding-agentsΒ· Added 22 Oct 2026

github.comrepoπŸ›‘οΈ Security

SnailSploit/Claude-Red

claude-red is a library of offensive security skills for the Claude Skills system, each a SKILL.md file that loads on conversational triggers (for example, mentioning SQL injection loads offensive-sqli). Categories include web, Active Directory, cloud, mobile, exploit development, fuzzing, privilege escalation, post-exploitation and AI. It targets about 130 skills across 23+ categories, with an install script and sparse-checkout install per category. Built on Sahar Shlichov's offensive checklists, MIT licensed.

ClaudeClaude CodeActive Directory
Kai AizenSahar ShlichovSnailSploit

Offensive Security, AI SecurityΒ· Added 22 Oct 2026

arxiv.orgpaper🧠 AI

CellTrack-Bench: Microscopic Cell Tracking Benchmark for Vision-Language Models

CellTrack-Bench is a benchmark that tests vision-language models on microscopic cell tracking and compares them with specialised trackers. It has 1,537 problems covering 9,041 cell-linking decisions, drawn from 15 cell-tracking datasets across four imaging modalities, with a hard subset built from failures shared by distinct algorithmic trackers. The authors compare environment harnesses, benchmark 9 closed-source and 13 open-weight models, and analyse failure modes.

vision-language modelLLM
CellTrack-BencharXiv

evals, multimodal, researchΒ· Added 24 Oct 2026, published 22 Oct 2026

arxiv.orgpaper🧠 AI

DuoCook: An Overcooked-Inspired Benchmark for Visual Planning and Coordination

DuoCook is an Overcooked-inspired benchmark in which one vision-language model controls two cooks from top-down views in Unreal Engine environments built with coding agents. It has 20 maps in five categories covering equipment contention, changing terrain and handoff dependencies. Four VLMs were compared; the best, gpt-6-astra, reached 26.2% mean order completion. A notebook memory ablation had mixed effects: positive for Claude and Qwen, negative for GPT and Gemini.

Unreal Enginevision-language model
DuoCookGPT-6 AstraClaude+4

evals, agents, multimodalΒ· Added 24 Oct 2026, published 22 Oct 2026

decrypt.coarticle🧠 AI

What Is a Neocloud? The GPU Clouds Powering the AI Boom

Decrypt explainer on neoclouds, specialist providers such as CoreWeave and Nebius that rent Nvidia GPU clusters for AI training and inference. It covers the chips, power and debt model, Bitcoin miners turned AI hosts, and customers including Microsoft, AWS, Google and Anthropic. It cites Gartner's 14 October 2026 forecast that over 80% of neoclouds will stop operating independently by 2030.

EthereumBitcoin
CoreWeaveNebiusLambda+22

ai-infra, ai-policyΒ· Published and added 22 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

Linear Cryptanalysis of TFHE-Friendly Cipher FRAST in the Average Key Setting

Linear cryptanalysis of FRAST, a TFHE-friendly stream cipher, in the average key setting. It fixes the false-positive problem left open in the earlier attack by Bak et al., showing key differences fall into five indistinguishable classes per round. The Contract algorithm recovers the master key for 10 rounds and, on weak keys of density 2^-11.8 to 2^-5.4, reaches full FRAST within the claimed security.

FRASTTFHE
Contract algorithmBak et al.linear cryptanalysis+1

otherΒ· Added 24 Oct 2026, published 22 Oct 2026

deepmind.googlearticle🧠 AI

Beyond tree cover: mapping the world’s forest types

Forest Typology (ForTy) 2020 is a global 10-meter map from Google DeepMind, Google Research, WRI and IIASA. It sorts land into six FAO-based classes: primary, naturally regenerating, planted, plantation, tree crops and agroforestry, and other land. The model uses AlphaEarth Foundations embeddings and about 1.7 million labeled locations. It was 90% accurate on forest type across 9,000+ expert-checked sites. An early 2017 to 2025 time series is on Earth Engine.

Google Earth EngineAlphaEarth Foundations
Google DeepMindGoogle ResearchWorld Resources Institute+7

models, multimodalΒ· Published and added 22 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Tech and Security Companies Respond to PHP2Shell Vulnerabilities

SecurityWeek roundup of responses to PHP2Shell, two critical unauthenticated RCE flaws (CVE-2026-109618, CVE-2026-109619) fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on 21 October 2026. It covers the exploitation timeline (first attempt 17 October), vendor exposure checks, Red Hat's lower 8.1 score against NVD's 9.8, detections from Cisco Talos, CrowdStrike and Corelight, and government alerts.

PHPAWSGoogle Cloud+3
CVE-2026-109618CVE-2026-109619PHP2Shell+6

Blue Team & Detection, AppSecΒ· Published and added 22 Oct 2026

x.comthreadπŸ›‘οΈ Security

Paul Dragoonis (@dr4goonis) on X

Social post summarising emergency patches for Node.js (4 high CVEs), PHP (2 critical) and nginx (3 critical). Node.js flaws include a Brotli decoder out-of-bounds write, a DNS truncation bug and two TLS hostname-verification bypasses. PHP has use-after-free and heap corruption bugs, and nginx has alias-rewrite and map-regex heap overflows plus an SSI-AIO use-after-free. It lists the fixed versions for each product.

Node.jsPHPnginx
CVE-2026-111497CVE-2026-105482CVE-2026-105483+8

AppSecΒ· Added 23 Oct 2026, published 22 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

The Good, the Bad, and the Noisy: A Systematic Analysis of Ring-Oscillator-Based Noise Generators

This IACR ePrint paper (2026/2597) systematically compares ring-oscillator-based additive noise generators, a hiding countermeasure against side-channel attacks. Experiments show many existing designs ignore output amplification and the risk of the noise being filtered out, so they lower signal-to-noise ratio too little. The authors give a guideline on inverter chain length, output amplification and frequency randomization, and build a tailored generator for an AES implementation that outperforms prior designs.

AES
Florian StolzDina HesseJulius Hermelink+2

Hardware & RFΒ· Added 24 Oct 2026, published 22 Oct 2026

latent.spacearticle🧠 AI

[AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months

This AINews issue (20 to 21 October 2026) leads with PHP2Shell, two PHP-engine memory-corruption bugs (CVE-2026-109618 and CVE-2026-109619). Calif researchers found them with GPT-5.6 Sol under OpenAI's Patch the Planet, and Wiz reportedly found them independently with Gemini 4 Argon. It reconstructs the two-month coordinated response, Cloudflare WAF stopgaps and NSA guidance, and the dispute over vetted researcher access to models. Only the first 40,000 of 114,281 characters were reviewed.

PHPWordPressDrupal+6
CVE-2026-109618CVE-2026-109619OpenAI+18

ai-policy, modelsΒ· Added 23 Oct 2026, published 22 Oct 2026

latent.spacearticleπŸ›‘οΈ Security

[AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months

AINews issue of 20-21 October 2026 whose top story reconstructs PHP2Shell, two PHP-engine memory-corruption flaws (CVE-2026-109618 and CVE-2026-109619) with reported pre-auth RCE against WordPress, Drupal and Joomla. It covers the two-month coordinated response, separate discovery by Calif/OpenAI (GPT-5.6 Sol) and Wiz (Gemini 4 Argon), Cloudflare's WAF stopgap and NSA guidance. It lists open gaps: fixed versions, leak details, exploitation versus scanning.

PHPWordPressDrupal+3
CVE-2026-109618CVE-2026-109619PHP2Shell+12

AppSec, AI SecurityΒ· Added 23 Oct 2026, published 22 Oct 2026

Showing 150 of 1210

Show more