Tanmay (@TanmayK_03) on X
DBHub, a database MCP server, had a read-only mode bypass in its SQL check. The check treated every `--` as a comment, but MySQL only starts a comment when whitespace follows it. A hidden write statement could therefore still run, and a prompt injection could trigger it. Fixed in version 0.22.6. Replies say enforcement belongs in database grants and that parser tests need to be dialect-specific.
 x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
- aiproduck (@aiproduck) on X
Ruflo is an MIT-licensed wrapper for Claude Code and Codex that adds agent swarms, vector memory and an MCP server. The plugin install writes no files to the workspace, while npx init adds a .claude/ directory, CLAUDE.md and hooks. The post warns that mods run with the account's permissions, so users should read them first. It gives no benchmarks or architecture detail.
x.comthreadPublished and added 30 Oct 2026🧠 AI - Prasenjit Sarkar (@stretchcloud) on X
A thread on Cloudflare's agent-readiness scan and the AgentReady.org open spec for "Agent Experience", developed with Vercel, Stripe, Auth0, Mintlify, Google, Netlify and Elementor. The scan grades whether agents can find a site (robots.txt, DNS), read clean Markdown, pass bot rules, and discover an MCP server or API catalog. One quoted example raised a score from 20 to 67 by shipping an API catalog with Link headers, an MCP server card, a skills index and an AI catalog file.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI  Rohan Paul (@rohanpaul_ai) on X
Rohan Paul's X post summarizes a TikTok paper on MCP attacks. LLM agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the user query, the server reply and the final answer. The attack works because agents read natural-language tool descriptions when choosing and ordering tool calls. The visible text is truncated and gives no success rates or defenses.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security- Rohan Paul (@rohanpaul_ai) on X
Rohan Paul's X post summarizes the paper "Log-To-Leak: Prompt Injection Attacks on Tool-Using LLM Agents via the Model Context Protocol", from TikTok researchers. It reports that MCP-using agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the query, server reply and final answer. The attack works through natural-language tool descriptions that agents read when choosing and ordering tools. The visible text is truncated.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security  Eddy (@ieddysun) on X
Expo's official skills package gives AI coding agents scoped instructions for building Expo apps. One command, npx skills@latest add expo/skills --skill '*', installs it for Cursor, Copilot and Windsurf, while Claude Code and Codex use their plugin marketplaces. Skills include expo-router, expo-animation, expo-upgrade and eas-update. The Expo MCP server adds live docs lookup, compatible dependency installs, EAS build monitoring and simulator screenshots.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI- Hakimi Eiqbal (@hakimieiqbal) on X
A practical reverse-engineering map by hakimieiqbal on X that picks tools by target: native binaries, .NET, Electron, iOS, firmware, WebAssembly and network protocols. It introduces REA (morluto/rea), which connects coding agents to RE tools, and lists MCP bridges for IDA Pro, Ghidra and radare2. It adds an evidence-first workflow and free courses such as pwn.college and OpenSecurityTraining2.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security - Hakimi Eiqbal (@hakimieiqbal) on X
A thread by Hakimi Eiqbal that maps reverse-engineering tools by target type: native binaries, Electron, .NET, iOS, firmware, WebAssembly and network protocols. Its AI sections cover REA (an open-source layer connecting coding agents to analysis tools) and MCP bridges for IDA Pro, Ghidra and radare2. It argues for an evidence-first workflow and gives a prompt that separates verified facts from hypotheses.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI  Kizuno18 (@Kizuno18) on X
Kizuno18's X post argues that the move from local stdio and Docker MCP servers to remote HTTP/SSE endpoints matures the Model Context Protocol in enterprise infrastructure. It lists three trade-offs: short-lived OAuth/JWT bearer tokens replace mounted admin credentials, deferred tool discovery avoids roughly 20k tokens of eager schema loading, and HCP Terraform enforces Sentinel/OPA policy, audit trails and approvals server-side. Opinion post with no benchmarks or code.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026🧠 AI Buchi Reddy B (@buchireddy) on X
Buchi Reddy B's X thread comments on Forever Security's research (Gal Weizman, Omer Samet) on coding agents. A web page silently writes a fake AGENTS.md or CLAUDE.md into a Downloads folder, and Codex and Claude Code follow it as project rules. Codex then wrote an attacker's MCP server into the machine-wide config, so one injection becomes a standing connection for every session. It asks whether teams inventory runtime MCP connections against approved lists.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security- Rohan Paul (@rohanpaul_ai) on X
Hi3D v1.0 (formerly Sparc3D) is an open-sourced image-to-3D model from Hi3D, which runs a closed v3.0 refining at 2048 cubes per side. In a test with 13 professionals in 3D algorithms, 562 judgments against eight other image-to-3D models favoured it 83.5% of the time. The thread also covers the Hi3D Agent and an MCP server for other agents. Back and bottom views were checked, where TRELLIS.2 collapsed a winged figure.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI  cubillas (@cubillas888) on X
The tweet relays Pillar Security research that opencode on Windows and WSL could run attacker-controlled code during remote MCP server OAuth sign-in. The fix shipped in opencode 1.18.33 on 28 September, with no advisory or CVE published. It advises users of remote MCP servers to update and review which servers they connect to. Technical details are not in the post.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security Nicholas Martin (@ndgmlondon) on X
X thread started by Nicholas Martin (#IAM) advising that MCP tool permissions be verified and scoped session tokens used to enforce least privilege against indirect prompt injection. Replies argue that token scoping does not solve the confused deputy problem, because an injection borrows the agent's legitimate authority. They recommend per-task tokens with short expiry, with the grant logged beside the call, and raise MCP server dependency supply-chain risk.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security David Gutierrez | Eng (@david_x_ai) on X
Thread on two October 2026 npm compromises: @subql/common 5.8.3 (5 October), published through GitHub Actions OIDC Trusted Publishing after the attacker tampered with the publish workflow, and tensorlake 0.5.144 (8 October), published by the project's own release workflow with valid provenance for about 1 hour 40 minutes. Both ran on install and stole cloud, GitHub, Kubernetes, Vault, SSH and .env credentials; tensorlake also took AI tool and MCP config. Its payload installed a gh-token-monitor service that deletes the home directory if the stolen GitHub token is revoked, so remove it before rotating.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security Benjamin👨💻 (@Hislordship_9) on X
Thread on Forever Security's finding that a planted Markdown "Engineering Work Guidelines" file in ~/Downloads made Codex add a "project-tools" MCP server to ~/.codex/config.toml. The server ran npm install function-color, a known malicious package, and started a child session with --dangerously-bypass-approvals-and-sandbox. Codex complied in over 90% of the firm's tests; Claude Code, via a CLAUDE.md setting ANTHROPIC_BASE_URL, about half. Advice: don't start agents in Downloads, review instruction files, and diff agent config.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security- David Gutierrez | Eng (@david_x_ai) on X
Thread on a critical opencode bug disclosed by Pillar Security on Oct 19. On Windows and WSL, a remote MCP server could run code during OAuth sign-in, because the server-chosen authorization URL was put unescaped into a PowerShell command, so a PowerShell subexpression executed. opencode fixed it in 1.18.33 on Sep 28 as a browser-launch refactor with no advisory or CVE. MCP Inspector published an advisory for the same bug class, and its fix needs a major bump of the open package.
x.comthreadAdded 27 Oct 2026, published 25 Oct 2026🛡️ Security - Big Bull (@BIGBULLapp) on X
5ire is a desktop AI assistant and MCP client that connects to OpenAI, Anthropic, Google, Mistral, Grok, DeepSeek and Ollama from one window. It has a local knowledge base and tool calls over Model Context Protocol. The tools feature needs Python, Node and uv installed because it runs a local MCP server; without them it works only as a chat client.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🧠 AI  ReignSwords (@ReignSwords) on X
A reviewer tests GenOffice, an open-source Office suite (10.7k GitHub stars), through its CLI only. Markdown to .docx took 3.8s, JSON to .xlsx took 0.9s with a live SUM formula, and .docx to PDF failed twice until Xvfb supplied a display. It has byte-preserving edits, a skill file for Claude Code and Codex, and 29 MCP tools. Downsides: a 188MB download that filled a 512MB /tmp, Electron in the PDF path, and unproven trust in tracked changes and rollback.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🧠 AI- Gökdeniz Gülmez (@ActuallyIsaak) on X
An X post showing how to have Codex train a small model on Apple silicon through the mlx-lm-lora MCP server and skill. It gives five setup steps (pip install with the mcp extra, npx skills add, locate mlx-lm-lora-mcp, codex mcp add). The prompt runs four pre-training trials on tiny-random/qwen3 with the mlx-community/recycling_the_web-1k dataset. Codex picks the optimizer and learning rate itself, and the result is a table with validation loss and the best adapter path.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🧠 AI  Prasenjit Sarkar (@stretchcloud) on X
Post explaining Claude's new support for MCP Tasks and Elicitations. A server returns a durable task handle instead of blocking. The client polls tasks/get every 250 ms to 30 s, and states are working, input_required, completed, failed or cancelled. Elicitations pause a task at input_required for human approval. It also notes Cloudflare's stateless MCP servers and Code Mode, and Sentry and Linear adoption.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🧠 AI EveryDev.ai (@EveryDevAi) on X
ToolUniverse, from ScientistTools, is an open-source (Apache-2.0) toolkit that gives any LLM one interface to more than 1,000 scientific tools, models and databases such as PubMed, UniProt and ChEMBL. It ships a native MCP server, a Python SDK and a tu CLI, plus 68 pre-built agent skills. The post says it works with Claude Code, Cursor, Gemini CLI and Windsurf.
x.comthreadPublished and added 24 Oct 2026🧠 AI- Yash Patil (@yvshpvtil) on X
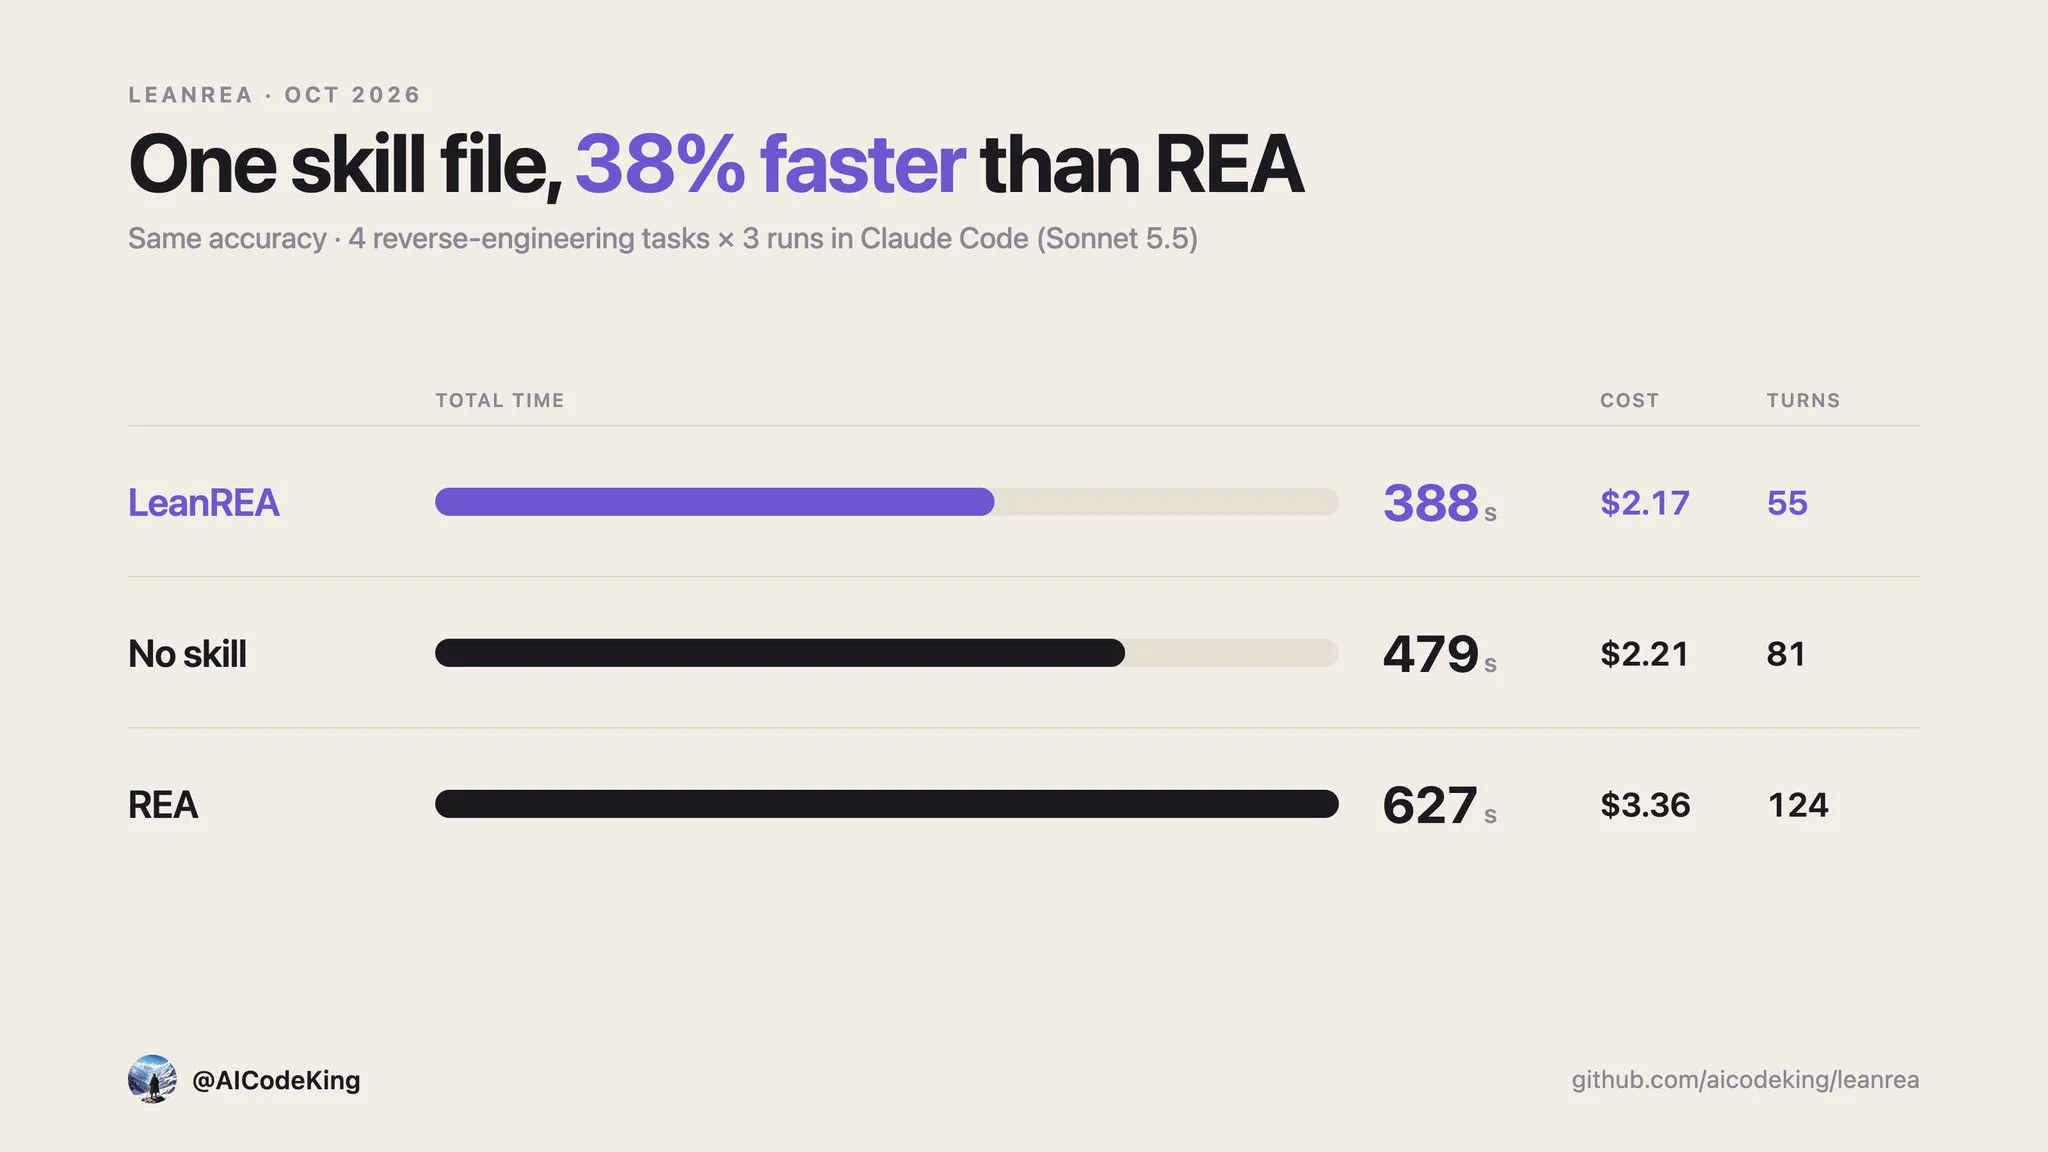
leanrea is an 8 KB skill file that tells a coding agent which plain CLI tools to use for reverse engineering, replacing REA, a 207-tool MCP server. In the author's test it ran 38% faster and 35% cheaper, scoring 74/75 against 75/75. The author lists caveats: 3 runs per task, one model, one machine, and Claude with no skill was already decent.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🧠 AI - Yash Patil (@yvshpvtil) on X
leanrea is an 8 KB skill file that tells a coding agent which plain CLI tools to use for reverse engineering, replacing the 207-tool REA MCP server. The author's test reports 38% faster, 35% cheaper, and a score of 74/75 against REA's 75/75. Caveats listed: 3 runs per task, one model, one machine, and Claude with no skill already performed decently. Replies question whether the lost point was a task where structured tool output beat parsing CLI text.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security - SpyTech Ai (@RizeOnline) on X
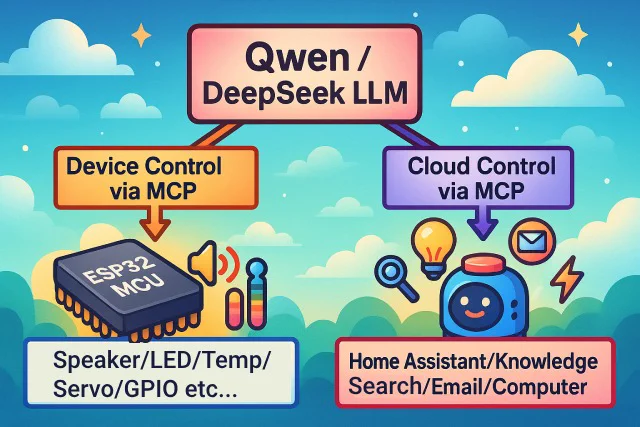
XiaoZhi ESP32 is an open-source, MIT-licensed firmware stack that turns ESP32 boards into MCP-based voice chatbots using models such as Qwen and DeepSeek. It streams Opus audio over WebSocket or MQTT + UDP through ASR, LLM and TTS, adds offline ESP-SR wake words, and uses device-side MCP to drive speakers, LEDs, servos and GPIO. It supports 138 board directories and builds with ESP-IDF 6.0.1 or newer.
x.comthreadAdded 23 Oct 2026, published 21 Oct 2026🧠 AI  VibecodersHQ (@VibeCodrHQ) on X
Post summarising Pillar Security's finding of a remote code execution flaw in OpenCode, the open-source AI coding agent. Versions 1.0.137 through 1.18.32 could run code from a remote MCP server during OAuth sign-in on Windows and WSL, with no prompt injection needed. The fix is in 1.18.33 (released 28 September). No advisory or CVE was issued, so scanners will not flag old installs. Interim advice is to remove unvetted remote MCP servers.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security- Swif (@swif_ai) on X
Swif (@swif_ai) reports that in the MCP TypeScript server SDK versions 2.0 to 2.2, a single server instance shared by several HTTP clients, which is the pattern the README shows, could send one client's responses to another client. Version 2.3.0 refuses this setup, so developers must build a server per request or per session. The post gives no CVE, advisory ID or technical detail.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security - Swif (@swif_ai) on X
A post from Swif (@swif_ai) on the MCP TypeScript server SDK versions 2.0 to 2.2. A single server instance shared across HTTP clients, the pattern shown in the README, could send one client's responses to another client. Version 2.3.0 refuses that setup, so servers must be built per request or per session. The post gives no code or advisory ID.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🧠 AI  Paulo Pierrondi | AI agents (@paulopierrondi) on X
Paulo Pierrondi's X post, part 9 of a series on installing MCP servers, lists a monthly review of installed servers. The checks are which tools the agent used, servers not called in weeks, overlapping tools that confuse the model, and whether each server still has an owner. A reply adds a decommissioning check: after removal, confirm the server's old credentials can no longer call the backend.
x.comthreadPublished and added 20 Oct 2026🧠 AI- DFIR Radar (@DFIR_Radar) on X
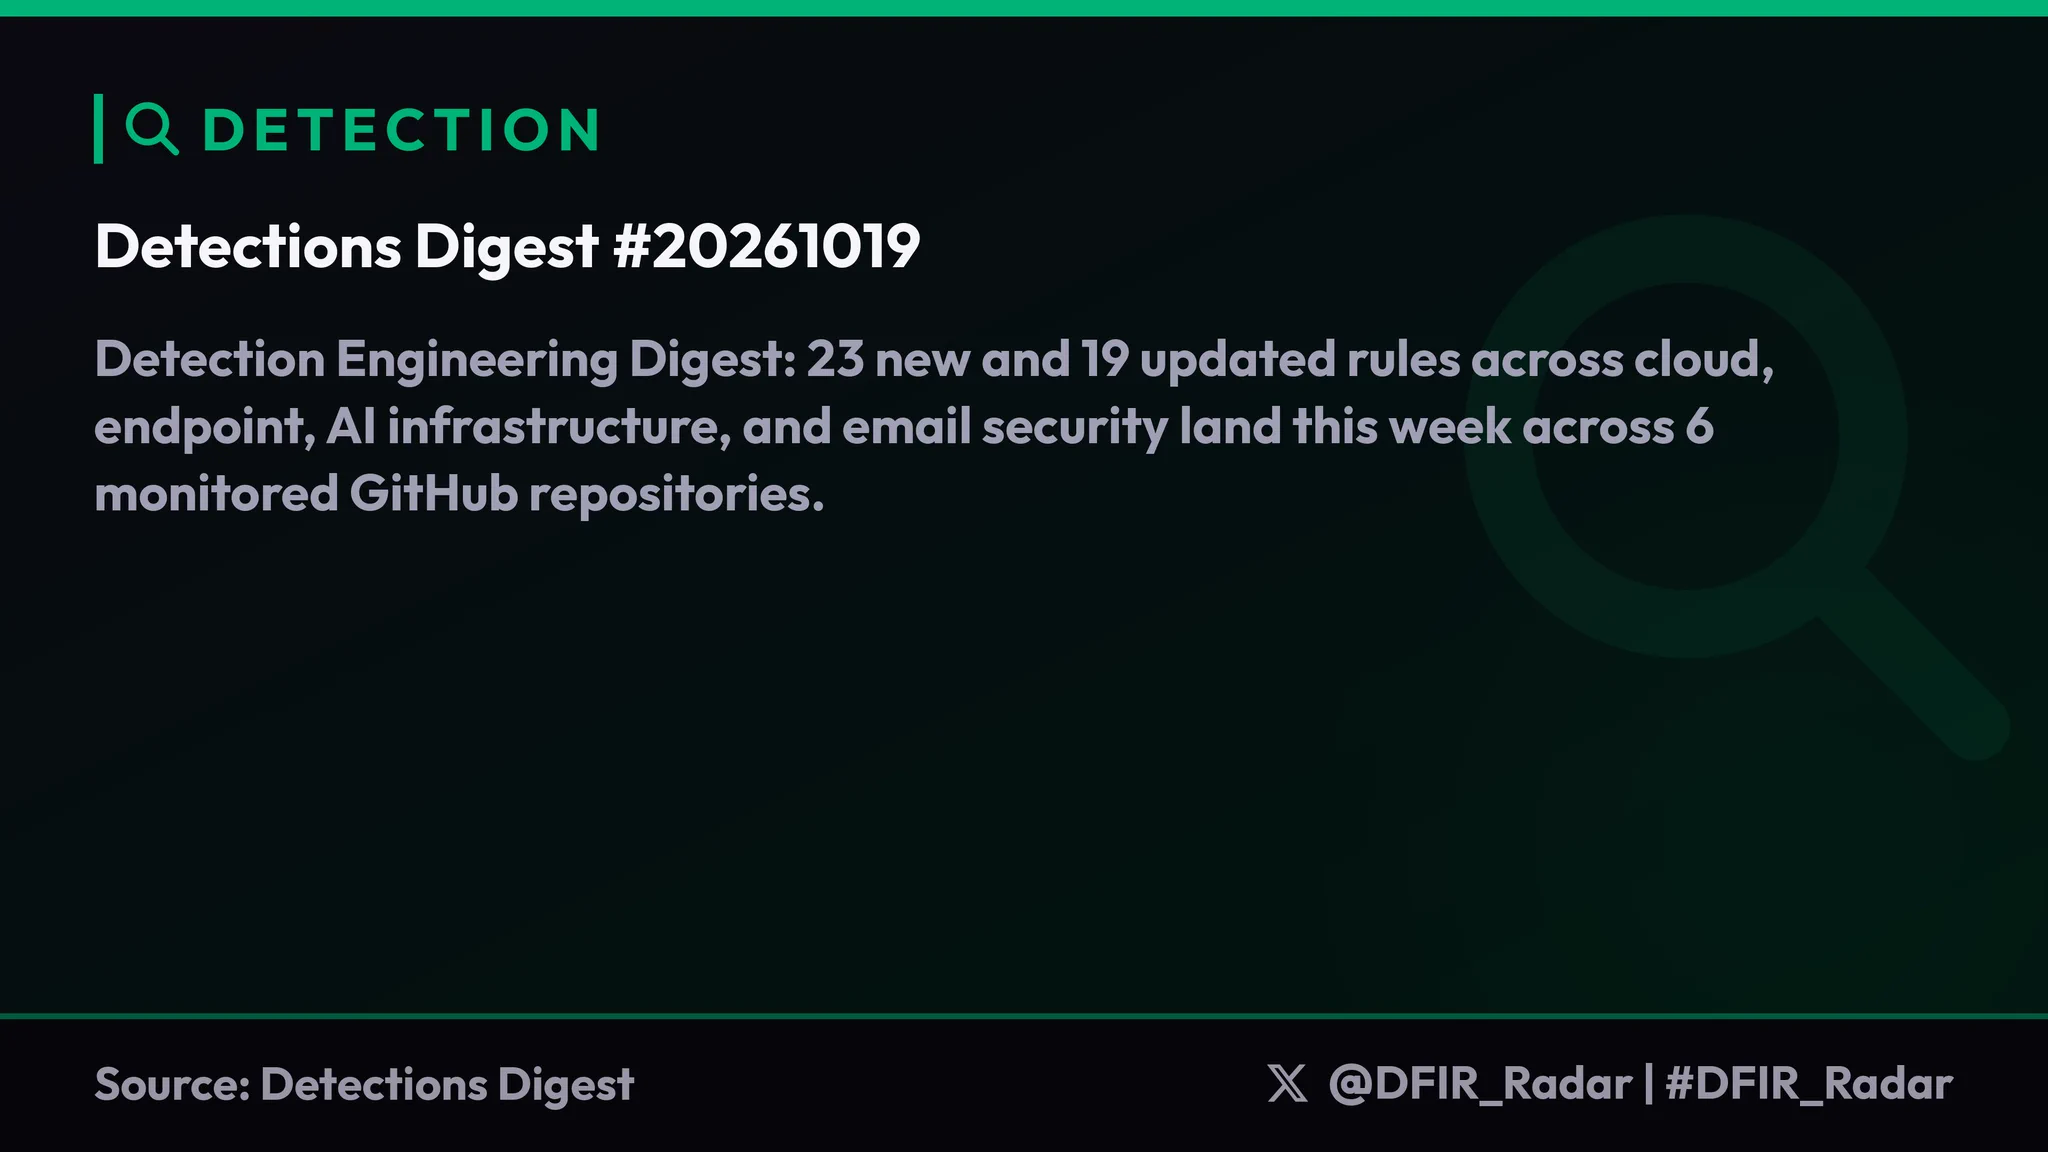
DFIR_Radar weekly detection engineering digest covering 23 new and 19 updated rules across 6 GitHub repositories. It lists KQL rules for Azure Key Vault secret retrieval, MCP client User-Agent bulk operations and local Azure token theft, AWS CloudTrail analytics, Sigma rules for firewall and ETW tampering (decimal 17 vs hex 0x11), updated LOLDrivers hashes, and Sublime email rules for OAuth consent phishing and fake IRS W-9 PDFs.
x.comthreadAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security  Angel (@ziran_pu) on X
AshAi, the AI package for the Elixir Ash Framework, is getting MCP client tools. Creating an MCP server with AshAi was already simple, but connecting your own LLM tool loop to an external MCP server had to be built by hand. The planned release includes OAuth client management resources. The post gives no release date, API details or code.
x.comthreadAdded 21 Oct 2026, published 19 Oct 2026🧠 AI Santhosh Patel (@santhosh_patell) on X
Summary of Pillar Security research on opencode, in which a malicious remote MCP server runs code on a Windows or WSL machine during the OAuth login step. The login URL goes unsanitised into PowerShell through the npm "open" package, so an https:// link containing $(...) executes. Affected versions are 1.0.137 to 1.18.32, fixed in 1.18.33 (28 September) as a "refactor" with no advisory or CVE. The behaviour was first reported in 2020 as a WSL 2 broken-link bug.
x.comthreadAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security FastFix AI (@FastfixAI) on X
FastFix AI thread giving six checks before installing a plugin, MCP server or skill for a coding agent. It starts from a 300K-star repo that an agent found writing to Claude Code, Codex and Copilot configs on install. Checks: read before running, inspect npm install scripts, verify the real repo against lookalike trojaned copies, pin versions, diff agent configs, and limit tokens and permissions.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security Magai (@HeyMagai) on X
Post from Magai (@HeyMagai) on Invariant Labs research showing that an approved MCP server can change its tool descriptions later without a new approval prompt, a "rug pull" like those in malicious code packages. It recommends pinning approval to tool definitions by hashing descriptions and re-prompting when the hash changes. For tools that move money, limits should stay server-side.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security- Steven Daugherty (@StevenDaugherty) on X
Post warning that FastMCP had a critical flaw where a malicious MCP server could execute code on the connecting client through a crafted tool schema. Fixed in FastMCP 3.4.8 and 4.0.11, and there is no patch for the 2.x line. It matters to anyone whose agents connect to MCP servers they don't control. The post gives no CVE ID or technical root cause.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🛡️ Security - Nicholas Martin (@ndgmlondon) on X
An X post advises auditing every MCP write tool against the database role it actually runs under. A shared service key lets prompt injection trigger unapproved writes, so each agent session should get a read-only role, with a test that writes are denied. Replies note that MCP servers often inherit ambient host credentials or can escalate through a second connection pool, and suggest also testing that another tenant's rows are unreadable with the same role.
x.comthreadAdded 18 Oct 2026, published 16 Oct 2026🛡️ Security  AmingIn_AI (@aming_inAI) on X
A tweet from AmingIn_AI describes a macOS screenshot-annotation tool. On release it saves the screenshot, a crop and the user's marks locally, then copies a 127.0.0.1 link. Claude Code or Codex on the same Mac can fetch that link and receive the marked image plus app/window info, and nothing is uploaded. It shows a local, privacy-preserving way to hand visual context to coding agents without MCP or cloud upload.
x.comthreadAdded 17 Oct 2026, published 16 Oct 2026🧠 AI- P.K. Sharma (@_pksharma) on X
Thread distinguishing two Langflow advisories on MCP Stdio command execution. CVE-2026-105740 (GHSA-7w94-79vh-5mr2) affects 1.8.3 and is fixed in 1.9.0, an authenticated non-admin path. CVE-2026-105697 (GHSA-w794-rj3p-xv45) covers 1.1.2 up to but excluding 1.10.3, with fixes in lfx and langflow-base too. The later fix validates the API, flow and pre-spawn boundaries and removes the shell wrapper, and the thread warns that LANGFLOW_AUTO_LOGIN=true can expose a token without credentials. It cites one sensor's telemetry (1,628 attempts from 28 IPs) with caveats, and gives a defensive checklist: verify patched packages, review stored MCP configs and imported flows, and hunt for unexpected child processes.
x.comthreadAdded 17 Oct 2026, published 15 Oct 2026🛡️ Security - Francis Santerre (@santerref) on X
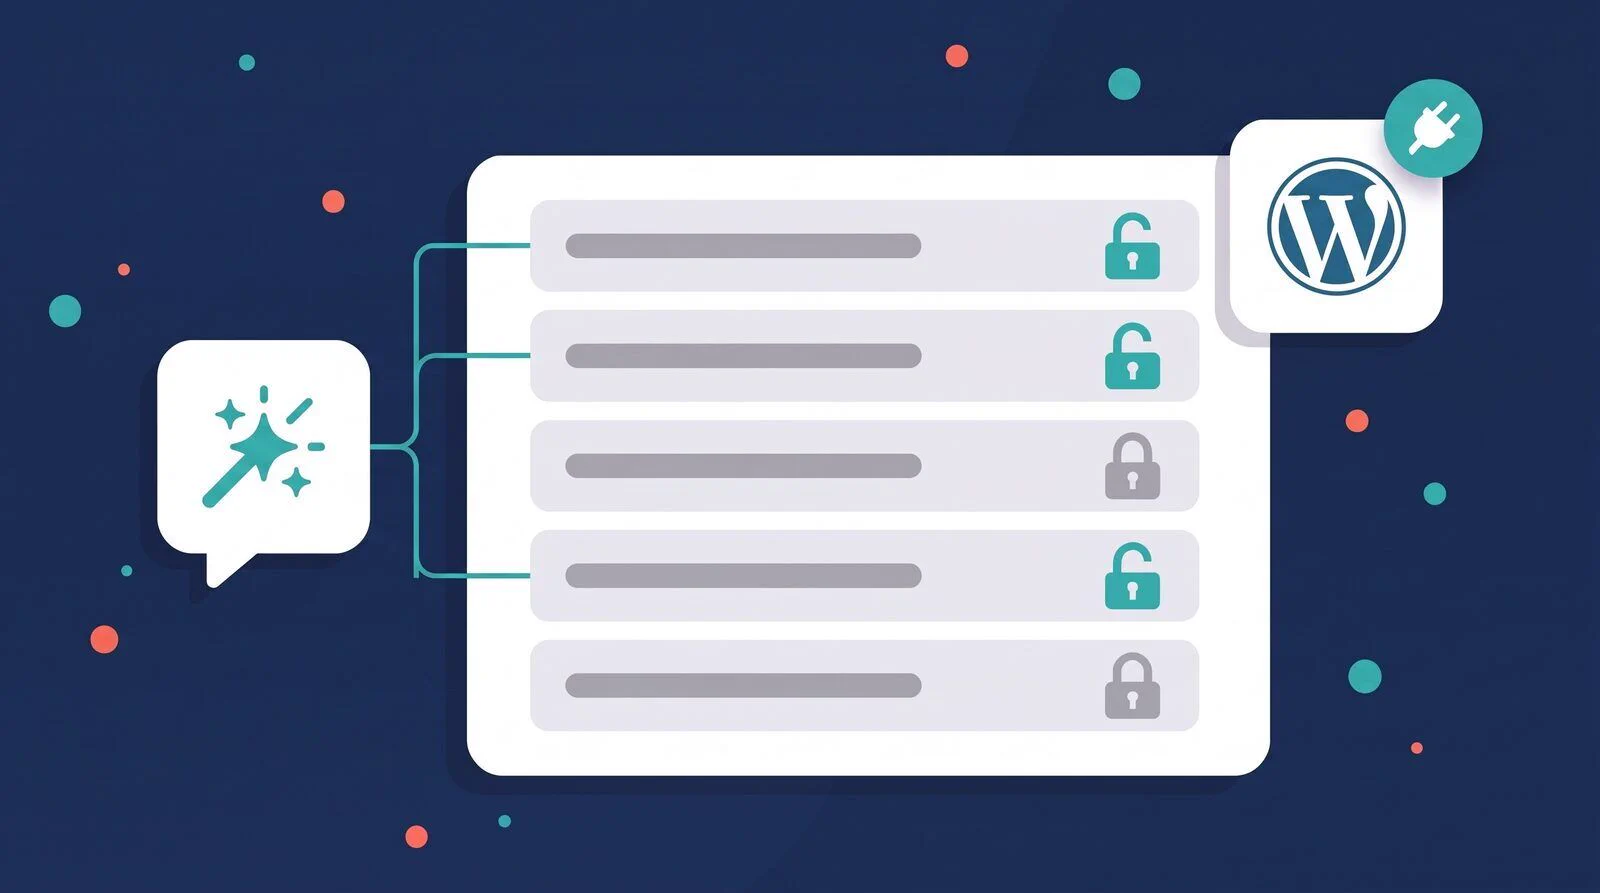
Post announcing that the MCP Adapter (0.7.0) is now a canonical plugin on WordPress.org, bridging the WordPress Abilities API to MCP. It exposes a default server at /wp-json/mcp/mcp-adapter-default-server, and only abilities a site marks public are exposed. The author's point is that the security review reduces to auditing the list of public abilities, which gives reviewers and pentesters a new endpoint to enumerate.
x.comthreadAdded 16 Oct 2026, published 15 Oct 2026🛡️ Security - Francis Santerre (@santerref) on X
Tweet announcing that the MCP Adapter is now a canonical plugin on WordPress.org (version 0.7.0). It bridges the WordPress Abilities API to the Model Context Protocol, with a default server at /wp-json/mcp/mcp-adapter-default-server. Only abilities a site marks public are exposed, so the security review comes down to auditing the ability list.
x.comthreadAdded 16 Oct 2026, published 15 Oct 2026🧠 AI - Victor (@VMG_CU) on X
A social post summarising Elastic's REF8801 campaign. A fake startup accelerator offered founders free Claude/Gemini credits plus a coding agent. The agent was a repackaged open-source project that set OPENROUTER_BASE_URL to an attacker-controlled endpoint and added its own MCP server, so victims' prompts and code went to the attacker. It shows how a trojanised AI coding agent can hijack the LLM base URL and add an MCP server for exfiltration.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026🛡️ Security - 44er (@44errrr) on X
Announcement of hexvero, an MCP server that gives coding agents a static first look at binaries and app bundles across 18 formats (ELF, PE, Mach-O, APK, .NET, Go, Wasm, Electron, SQLite). It uses zero-dependency Node parsers and marks each finding confirmed or inferred with file and line. Its tool catalog is 3,043 tokens, against a claimed 509,696 for the established reverse-engineering MCP server. Paged output with a byte budget shrinks a 541 MB Electron app to a 15 KB result, 1.3 MB of JSON to 7.9 KB, and a 450 KB build diff to 1.2 KB. radare2, rizin or Ghidra plug in for disassembly, and `npx hexvero setup --apply` registers it with Claude Code, Cursor, Codex and 15 more clients. It is a concrete example of keeping MCP tool definitions and results small enough for an agent's context window.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026🧠 AI  ERC-8444: Agentic Resource Discovery (ARD) Onchain
An Ethereum Magicians proposal for ERC-8444, which adds an onchain value and settlement layer under Google's Agentic Resource Discovery (ARD) spec for finding MCP servers, A2A agents, skills and APIs. A thin kernel records kind (skill, task, agent, registry), a CAIP-19/CAIP-10 anchor, a JCS+SHA-256 descriptor hash, a canonical URN and a status. Authority belongs to the paid address, and domains act as collected endorsements through /.well-known/ard.json. The reference implementation has Foundry-tested Solidity adapters and a Node.js gateway that passes the official ARD conformance CLI. It introduces a "task" kind (application/ai-task+json) for tenders aimed at suppliers, and the author asks for feedback on the trust root, the hash scope, same-chain anchors and the task payload.
 ethereum-magicians.orgthreadAdded 14 Oct 2026, published 13 Oct 2026🧠 AI
 Phillip Shoemaker (@pbsIdentity) on X
Social thread reacting to a newly disclosed high-severity OAuth vulnerability in the Model Context Protocol Python SDK, where a malicious MCP server could manipulate the authorization flow and steal credentials used by an agent. The author uses it to argue that delegated agent authority needs provenance (who granted it, to which agent, for which service and resource, whether it is transferable or replayable, and when it expires) and that machine-to-machine trust must be auditable by humans. Gives no CVE ID or technical exploit detail.
x.comthreadAdded 13 Oct 2026, published 12 Oct 2026🛡️ Security- =dennis; (@Xidea404) on X
A tweet from @Xidea404 pointing to the ADI Chain MCP Server documentation on docs.adi.foundation. The server lets AI agents interact with the ADI blockchain through the Model Context Protocol. The tweet carries no technical detail itself, so what the server exposes can't be confirmed from it. It is a pointer to a blockchain-specific MCP connector.
x.comthreadPublished and added 12 Oct 2026🧠 AI  Nicholas Michael Kloster (@showxlate) on X
A researcher announces a zero-click indirect prompt injection RCE in REA (Reverse Engineering Assistant), an MCP tool. Analyzing a malicious web target silently exfiltrates AWS keys, GitHub tokens and SSH identities. The stated root cause is that process.env is passed unconditionally to child processes, so the full environment is exposed to attacker-driven commands. A full writeup is promised but not yet published; replies add unverified skepticism about the project's provenance.
x.comthreadAdded 13 Oct 2026, published 12 Oct 2026🛡️ Security- Jetwani Avinash (@jetwaniavinash) on X
Announcement of jevmem, an open-source MIT plugin that gives Claude Code, Cursor and Codex persistent project memory. After each turn it asks Jev (a TypeSafe AI model) whether anything is worth keeping (a rule, decision, failure, or to-do) and writes one line to a plain Markdown file tracked in git. It also checks commands against saved rules before they run and asks first, or blocks. Reported results: Claude followed the rule in 66 of 72 sessions vs 28 without it, the right save/skip call on 98.5% of 66 turns, and 66 of 68 rule-breaking commands caught out of 274 test commands. Listed in Anthropic's Claude plugin directory and on the MCP Registry.
x.comthreadPublished and added 10 Oct 2026🧠 AI - 0xMarioNawfal (@RoundtableSpace) on X
A tweet highlighting Prompts Chat (formerly Awesome ChatGPT Prompts), an open-source prompt library on GitHub that the post says has 167K+ stars. It works across ChatGPT, Claude, Gemini and other models. The post lists a CLI, an MCP server, a Claude Code plugin and self-hosting with custom branding and auth, all free. It is worth cataloguing as a pointer to a widely used prompt collection that now plugs into coding-agent and MCP workflows.
x.comthreadPublished and added 10 Oct 2026🧠 AI  Richard Abishai (@richardabish_ai) on X
An X post by the creator of ROPE, a prompt-injection benchmark for LLM agents. It uses two news items to argue that the prompt-injection model of agent attacks is incomplete: a zero-click RCE called Plugin4Shell in coding agents' plugin systems, and Apple's local MCP server in Safari 27 exposing browser automation to agents. Neither involved persuading a model. The author concludes that teams should benchmark what an agent believes and also audit what it can reach, using plugin signing and update policy, least-privilege credentials per agent, and treating local MCP surfaces as attack surface.
x.comthreadPublished and added 9 Oct 2026🛡️ Security- James Berthoty (@JamesBerthoty) on X
James Berthoty argues that AI guardrails for first-party AI features should be treated as an extension of cloud/product security, not tied to employee-usage monitoring. Guardrails (prompt injection defense, content filtering, goal alignment) are available from AI security vendors, gateways, frontier providers and SDKs. He recommends deploying in-depth guardrails through developer SDKs or an existing cloud runtime/CADR provider, because those see what happens on the workload (such as a prompt injection leading to workload takeover, or the files a malicious MCP call wrote). Dedicated AI security vendors offer an integrated policy engine and deeper AI red-teaming, but they are usually run by internal IT rather than cloud/product security teams.
x.comthreadAdded 10 Oct 2026, published 8 Oct 2026🛡️ Security - Dr Milan Milanović (@milan_milanovic) on X
A Twitter/X thread breaking down three protocols that connect AI agents to different things: MCP (agent to tools/data, JSON-RPC 2.0 over stdio or Streamable HTTP), A2A (agent to agent, using an Agent Card JSON manifest at /.well-known/agent-card.json, running over JSON-RPC/gRPC/HTTP+JSON), and ACP, the Agent Client Protocol created by Zed in 2025 for connecting code editors to coding agents (modeled on LSP, JSON-RPC over stdio). It clarifies that IBM Research's older "Agent Communication Protocol" (also abbreviated ACP) merged into A2A on 29 August 2025, making many existing protocol comparisons outdated, and notes governance differences: MCP and A2A sit under the Agentic AI Foundation (Linux Foundation) while the Agent Client Protocol is governed by Zed and JetBrains. The author also mentions building an internal MCP server letting customers run and schedule reports via ChatGPT and Claude.
x.comthreadPublished and added 7 Oct 2026🧠 AI - Prasenjit Sarkar (@stretchcloud) on X
Describes Uber's internally-built ADR (Agentic Detection & Response) system, open-sourced in August with an MLSys paper, which monitors over 50,000 daily AI agent sessions via an MCP-based sensor inside Cursor, Claude Code and Codex. Uber found 206 credential exposures in ten months from normal agent use (not prompt injection), and ADR hits 100% detection with 3 false positives on the public AgentDojo benchmark; the thread also flags that human approval fatigue breaks down as a safety control past roughly 50 agent actions per session.
x.comthreadPublished and added 6 Oct 2026🛡️ Security  Bill Xie (@joyrap) on X
A Twitter thread summarizing key takeaways from a podcast conversation with Thibault Sottiaux (Tibo), Head of ChatGPT and Codex at OpenAI. Topics include the prediction that most internet actions will soon be taken by agents, how Notion's MCP server launch caused a traffic flood that strained its systems, the likely disappearance of the model picker in favor of automatic routing, skepticism about loops and graphs as durable agent architectures, and OpenAI's approach to AI safety.
x.comthreadPublished and added 5 Oct 2026🧠 AI Register Codex's Computer Use as a Claude Code MCP Server
A thread shows how to register Codex's built-in Computer Use capability — the "cua_repl" MCP server found in ~/.codex/plugins/cache/openai-bundled/unified-computer-use/ — as a custom user MCP server (named "codex-cu") inside Claude Code, letting Claude drive Mac GUI automation via Codex's computer-use backend instead of a separate CUA driver. The author reports an informal benchmark across 8 computer-operation tasks: Claude Opus 5.5 + Codex Computer Use scored 6/8, Codex alone scored 6/8, and the original CUA driver only scored 3-4/8, with a caveat that future Codex updates could break this cross-agent MCP reuse.
x.comthreadPublished and added 5 Oct 2026🧠 AI SunsetSyntax (@sunsetsyntax) on X
A short account of switching from a split Neo4j (relationships) + separate vector DB (embeddings) setup — which required manually reconciling IDs whenever an agent wrote a fact — to NornicDB, a single Go-based graph+vector store that speaks Bolt/Cypher and bundles an MCP server in one process. The point is that agents can query a unified memory store without an app layer babysitting two separate databases.
x.comthreadPublished and added 4 Oct 2026🧠 AI- Jan Curn (@jancurn) on X
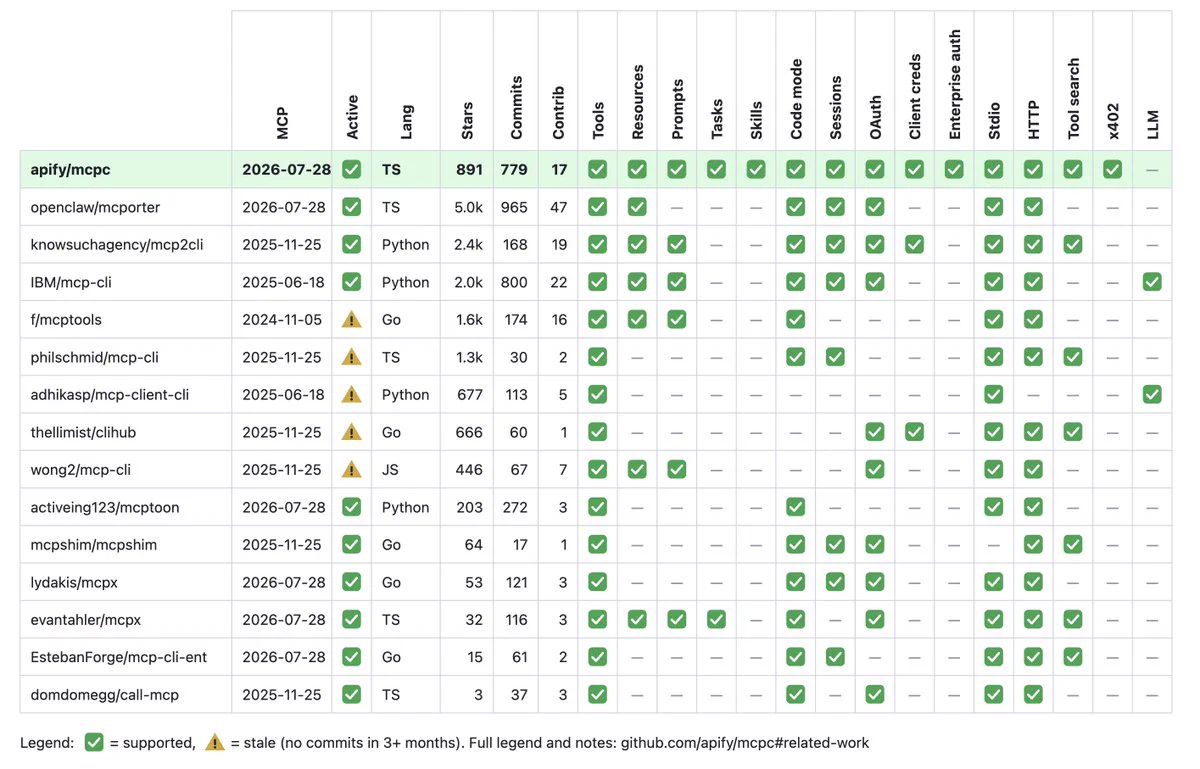
Announcement of mcpc v0.7.0, Apify's open-source MCP CLI client (npm i -g @apify/mcpc), which adds support for the MCP Skills extension with new skills-list/skills-get commands that verify SKILL.md and supporting files against the skill manifest via size and SHA-256 checks before printing content. The release also ships security hardening: repo-local .mcp.json auto-discovery can no longer read environment variables (blocking leaks like $GITHUB_TOKEN), OAuth refresh tokens are now scoped only to the auth server originally used, and Windows login URLs no longer launch through cmd.exe.
x.comthreadAdded 5 Oct 2026, published 3 Oct 2026🛡️ Security - Jan Curn (@jancurn) on X
Jan Curn announces mcpc v0.7.0, an open-source MCP CLI client (npm package @apify/mcpc), adding support for the MCP Skills extension via new skills-list and skills-get commands that fetch and cryptographically verify SKILL.md and supporting files against the skill manifest (size + SHA-256). The release also hardens security by preventing repo-local .mcp.json auto-discovery from reading environment variables (blocking token-leak tricks), scoping refresh tokens to the originating auth server, and fixing an insecure Windows login URL launch path via cmd.exe, alongside OAuth session longevity fixes and 2026-07-28 MCP spec compatibility improvements.
x.comthreadAdded 5 Oct 2026, published 3 Oct 2026🧠 AI  Nation (@visitnation) on X
NATION Guard is a local, open-source tool announced by Nation that inspects the instructions and configuration behind AI agents. It combines injection-pattern scanning, integrity baselining, and per-server MCP fingerprinting so developers can detect suspicious prompt injections and unauthorized changes to their agent setup.
x.comthreadPublished and added 3 Oct 2026🛡️ Security Dave Gilbert (@docgotham) on X
A Twitter/X thread reacting to OpenAI's announcement that ChatGPT Sites can now host MCP servers, including turning plugin extensions into deployable MCP servers (e.g. "@sites create a todo list that I can use in ChatGPT"). User Dave Gilbert (@docgotham) flags a concrete operational bug: with a ChatGPT Pro account, custom MCP servers can't be refreshed — disconnecting/reconnecting or even deleting and re-adding a server still serves the old cached plugin version after an update.
x.comthreadPublished and added 2 Oct 2026🧠 AI- Average AI Bro (@AverageAiBro) on X
An X post presenting Reversecore MCP, an MCP server that wraps authorized reverse-engineering, malware-analysis, forensics and SAST-style tools such as radare2. The user picks a profile, points it at a sample, and the agent gets structured results back in the session without driving the tools by hand. It is a concrete example of profile-based tool exposure for specialized toolchains, offered as a free alternative to a commercial IDA setup. The post stresses authorized analysis only.
x.comthreadAdded 1 Oct 2026, published 30 Sep 2026🧠 AI - Average AI Bro (@AverageAiBro) on X
Claude Code added a `claude --desktop` command that opens the Desktop app on the current directory or a resumed/continued session, plus `claude plugin configure` to view a plugin's options. Bundled .mcpb MCP servers can now have their settings set at `plugin install --config` time so they start immediately without a manual Configure step. The post also notes CLAUDE_CODE_DISABLE_WEB_FETCH to disable WebFetch and an allowedProviders setting to restrict which API providers a managed machine can use.
x.comthreadPublished and added 30 Sep 2026🧠 AI - Stevan Bogosavljević (@stevyhacker) on X
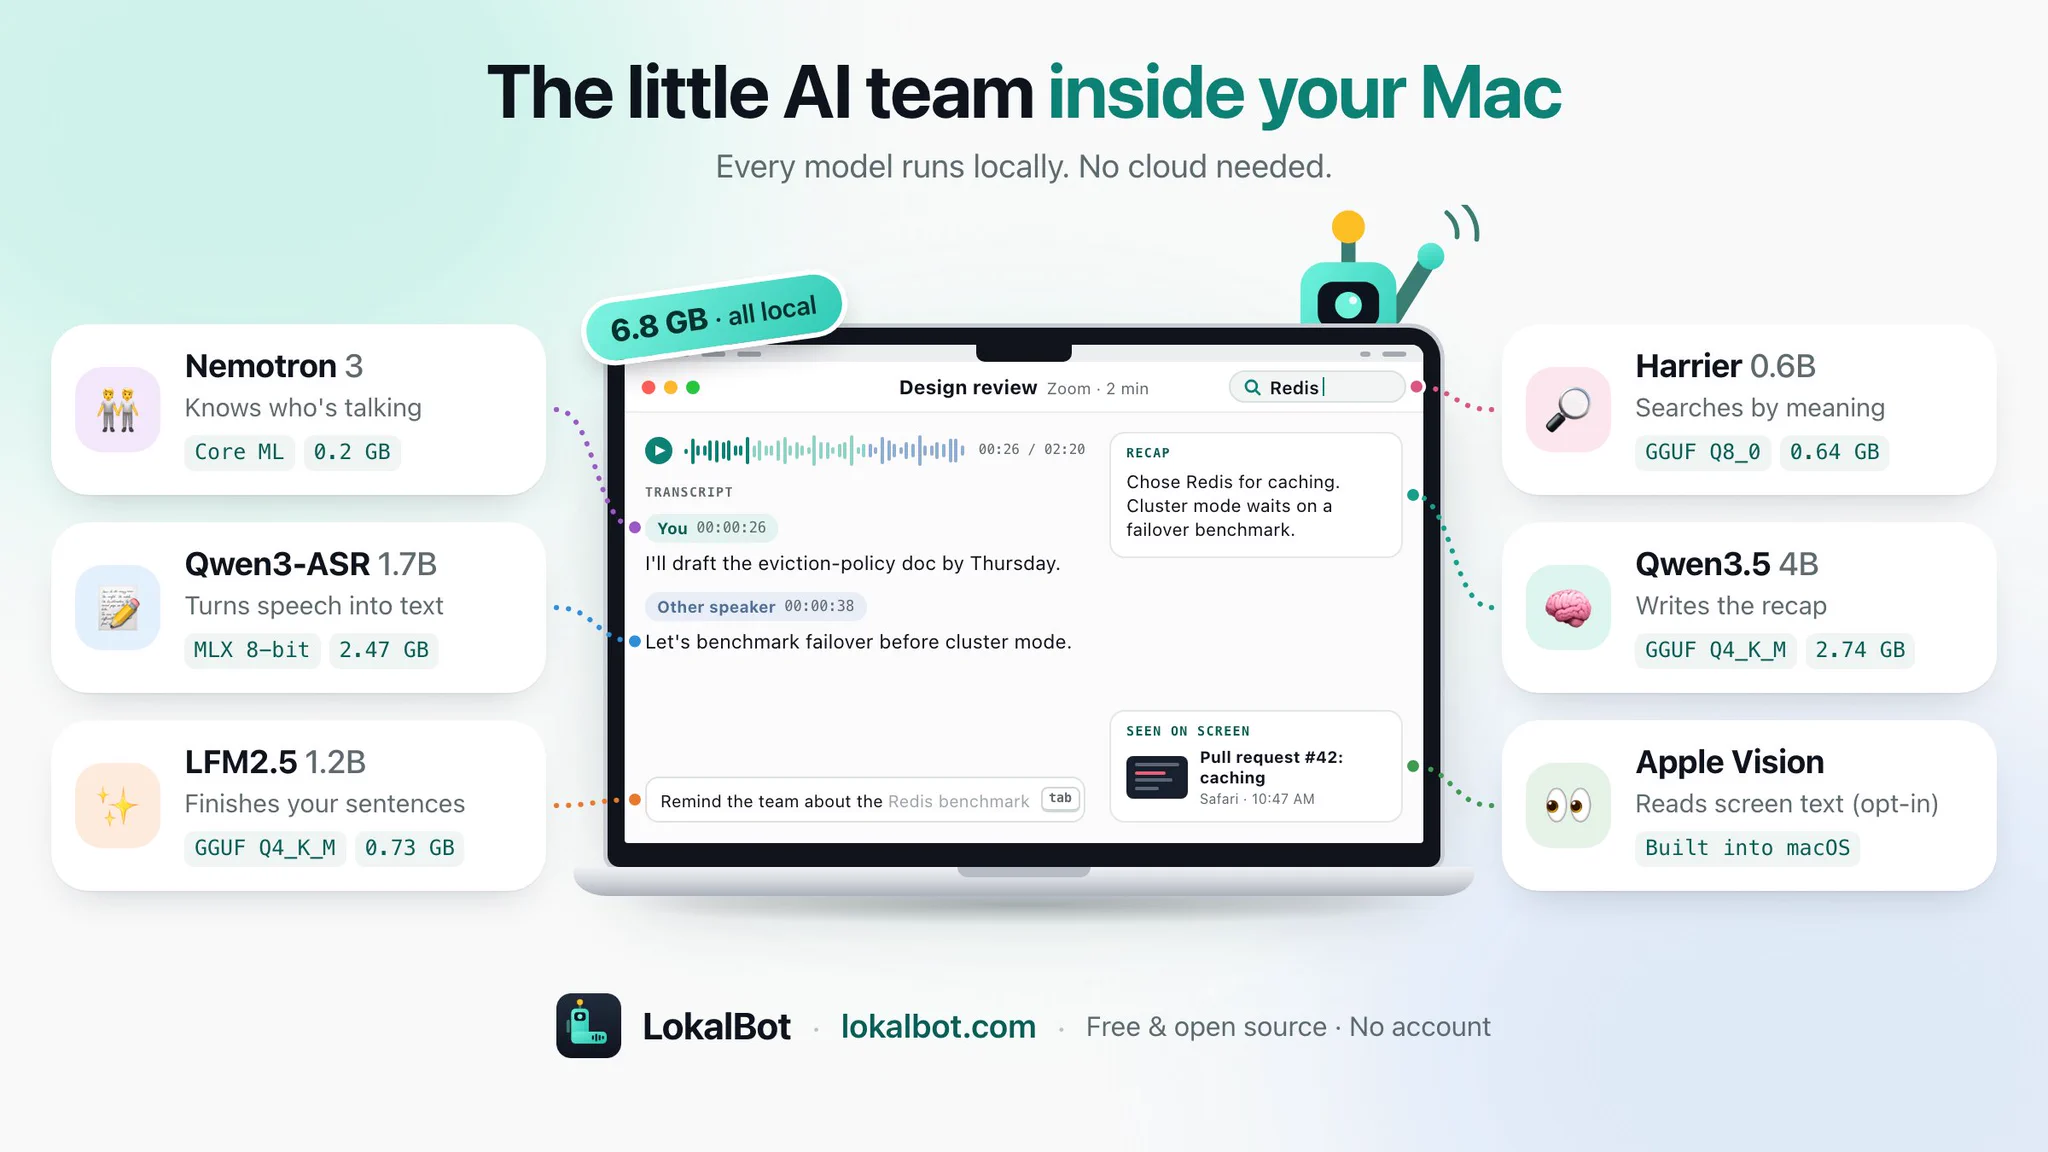
LokalBot 0.9.2 is a free, open-source local-first assistant that records meetings and screen activity, using five small open-weight models chained together entirely on a MacBook (6.8 GB total): Nemotron 3 for speaker diarization, Qwen3-ASR 1.7B for transcription, LFM2.5 1.2B for sentence completion, Harrier 0.6B for semantic search, and Qwen3.5 4B for recap generation. It exposes this captured 'memory' to Claude Code and Codex through an MCP server or CLI, letting coding agents pull context from past meetings and screen content.
x.comthreadPublished and added 30 Sep 2026🧠 AI - 0xor0ne (@0xor0ne) on X
A tweet from @0xor0ne surfacing two blog posts by researcher ZephrFish on using LLMs for vulnerability research: one describing an MCP (Model Context Protocol) server for the workflow, and a second on 'harnessing' LLMs for this purpose. The posts (hosted at blog.zsec.uk) cover applying LLM agents to vulnerability discovery/analysis tasks.
x.comthreadPublished and added 9 Sep 2026🛡️ Security - Dhairya Karekar (@dkare1009) on X
An X thread summarizing a 1-hour Google course on agentic engineering, covering building a first AI agent, agent memory (short-term, persistent, long-term), agentic loops for long-running agents, MCP vs API for tool use, and multi-agent systems. The thread's value is framing these as one integrated system rather than separate tricks, which the poster argues is where most agent-building guidance falls short.
x.comthreadAdded 22 Sep 2026, published 31 Jul 2026🧠 AI