Skip to content

126 results for β€œKev”

What you seeeverything
x.comthreadπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

CVE-2026-102764 is an unauthenticated RCE in BeyondTrust Remote Support, already exploited and in CISA KEV. Rapid7 published an analysis and opened a Metasploit pull request on 30 October 2026, showing code execution on version 24.1.2 via a forged "local" message origin, the native file-transfer service and a PHP file written to the web root. BT26-05 (CVSS 4.0 9.3) is fixed by patch BT26-05-RS; SaaS was patched by 9 October.

BeyondTrust Remote SupportMetasploitPHP+1
CVE-2026-102764CISA KEVRapid7+2

Offensive Security, Threat Intel, AppSecΒ· Added 1 Nov 2026, published 31 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA added two Ivanti Connect Secure vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog on 30 October 2026, citing evidence of active exploitation: CVE-2026-111357 (missing authentication for a critical function) and CVE-2026-118527 (generation of predictable numbers or identifiers). The alert restates BOD 26-04, which requires federal civilian agencies to remediate KEV-listed flaws on exposed assets and check for prior compromise. It also links the KEV nomination form.

Ivanti Connect SecureCISA KEVVPN
CVE-2026-111357CVE-2026-118527BOD 26-04+1

Threat Intel, GRCΒ· Published and added 30 Oct 2026

bleepingcomputer.comarticleπŸ›‘οΈ Security

CISA says max severity GitLab flaw now exploited in the wild

CVE-2026-97229 is a maximum-severity GitLab flaw in the CI/CD Regular Expression Compiler, caused by an integer overflow, that lets unauthenticated attackers run code via a crafted regular expression. CISA added it to the KEV Catalog and ordered federal agencies to patch under BOD 26-04. GitLab fixed it in CE/EE 19.4.2, 19.3.5 and 19.2.8, and Shadowserver tracks about 2,800 exposed CE instances.

GitLab
CVE-2026-97229CVE-2026-0723CVE-2026-110264+10

AppSec, DevSecOps, Threat IntelΒ· Published and added 30 Oct 2026

bleepingcomputer.comarticleπŸ›‘οΈ Security

Drupal warns of critical Commerce Core flaw exploited in attacks

Drupal Commerce Core has a critical missing-authorization flaw, CVE-2026-118539, that unauthenticated attackers exploit in the wild. It affects versions 0.0.0 to 2.41 and 3.0.0 to 3.3.13. Drupal urges upgrading to 3.3.13 (or 8.x-2.41 on the older branch) and auditing orders for inconsistencies. The article also recalls CVE-2026-9082, exploited in May and added to CISA KEV, and two RCE patches (CVE-2026-108097, CVE-2026-108099).

DrupalDrupal Commerce Core
CVE-2026-118539CVE-2026-9082CVE-2026-108097+3

AppSec, Threat IntelΒ· Published and added 30 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge CVE of the Day #091 covers Progress WS_FTP Server CVE-2026-84295 (unauthenticated administrator-credential exposure, CVSS 10.0) and CVE-2026-90868 (conditional OS command and argument injection, CVSS 9.9, low privileges). Fixed floors are 2024.0.7/9.0.7 and 2025.0.4/10.0.4; 2024.0.6/2025.0.3 fix only the first. It gives KEV, EPSS and SSVC status, six SOC checks, and Windows 4688 evidence queries.

WS_FTP ServerWindowsPowerShell+3
CVE-2026-84295CVE-2026-90868CWE-287+9

Blue Team & Detection, Identity & AccessΒ· Added 2 Nov 2026, published 30 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Max-Severity GitLab Vulnerability Exploited Against Alpine Linux

CVE-2026-97229 is a CVSS 10 code execution flaw in Onigmo, Ruby's regular expression engine, reachable through crafted CI/CD configuration in GitLab. Attackers used it against Alpine Linux's GitLab on 20 and 21 October 2026 and failed; Alpine rebuilt the instance and found no tampering with aports or packages. Self-managed installs with their own Ruby need Ruby 3.3.13, 3.4.12 or 4.0.9, not just GitLab 19.3.6. CISA added it to KEV.

GitLabRubyOnigmo+2
CVE-2026-97229CISA KEVBOD 26-04+1

AppSec, Threat Intel, DevSecOpsΒ· Published and added 30 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA alert of 29 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities catalog on evidence of active exploitation: CVE-2026-97229, an integer overflow in GitLab CE/EE, and CVE-2026-76418, a NULL pointer dereference from an unchecked return value in Cisco Secure Firewall ASA and FTD. It restates BOD 26-04 remediation duties for federal civilian agencies and links the KEV nomination form.

CISA KEVGitLabCisco Secure Firewall ASA+1
CVE-2026-97229CVE-2026-76418BOD 26-04+3

Threat Intel, GRCΒ· Published and added 29 Oct 2026

blog.talosintelligence.comarticleπŸ›‘οΈ Security

A quiet week in infosec <.<

Cisco Talos Threat Source newsletter for the week of the PHP and Node.js vulnerability news cycle. It summarises NIK C2, a Go-based Windows implant that dumps credentials, streams keystrokes, deploys screen-locking ransomware and uses a victim's hijacked OpenAI API keys to analyse stolen data. It also lists weekly headlines (CISA KEV PHP bugs, Brotli flaw, Gheist GitHub token theft), Talos links and top malware hashes.

GoWindowsOpenAI+3
NIK C2PHP2ShellNode2Shell+7

Threat Intel, AI SecurityΒ· Published and added 29 Oct 2026

bleepingcomputer.comarticleπŸ›‘οΈ Security

CISA warns of Fragnesia Linux flaw chained in PHP2Shell attacks

Fragnesia (CVE-2026-46300) is a Linux kernel XFRM ESP-in-TCP logic bug in the Dirty Frag class that gives local attackers root, with a public PoC. CISA added it to the KEV catalog and ordered federal patching under BOD 26-04. Attackers chain it with PHP2Shell (CVE-2026-109618, CVE-2026-109619) to implant PHP webshells. Dream Security tied the chain to 25 rooted servers in the US, Japan, Taiwan and South Korea.

Linux kernelLinuxPHP+1
CVE-2026-46300CVE-2026-109618CVE-2026-109619+9

Threat Intel, Offensive SecurityΒ· Added 30 Oct 2026, published 29 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-103780 is a stack-based buffer overflow (CWE-121) in Dell PowerProtect Data Domain / DD OS. An unauthenticated remote attacker could get command execution (CVSS 3.1 9.8, Dell DSA-2026-416). The post lists affected and fixed builds for four release trains (Feature Release, LTS2024, LTS2025, LTS2026). It adds KEV, EPSS and SSVC status, plus six defensive checks. The vulnerable service is not public.

Dell PowerProtect Data DomainDD OSCVSS+2
CVE-2026-103780CVE-2026-86400CVE-2026-86397+5

Blue Team & Detection, Cloud & InfraΒ· Added 31 Oct 2026, published 29 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Chinese Hackers Quietly Used Low-Severity ESXi Logging Flaw as Zero-Day

CVE-2026-41709 is a low-severity insufficient-logging flaw in VMware ESXi that lets a logged-in administrator perform operations without audit entries. CISA added it to the KEV catalog, and CrowdStrike reported that China-nexus actor Warp Panda used it as a zero-day against US organizations, including law firms, to cut audit visibility. The article also covers exploitation of vCenter bugs CVE-2026-59309 and CVE-2026-59310 and lists the fixed ESXi builds.

VMware ESXiVMware vCenterCrowdStrike
CVE-2026-41709CVE-2026-59309CVE-2026-59310+10

Threat IntelΒ· Published and added 29 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA alert of 28 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities Catalog on evidence of active exploitation: CVE-2026-41709 (Broadcom VMware ESX insufficient logging) and CVE-2026-46300 (Linux kernel missing variable initialization). It restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise. It also links the KEV nomination form.

CISA KEVVMware ESXLinux kernel
CVE-2026-41709CVE-2026-46300BOD 26-04+1

Threat Intel, GRCΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comthreadπŸ›‘οΈ Security

Christiaan Stoudt (@cstoudt) on X

Thread on CVE-2026-97631, a critical (9.5) flaw in TianoCore EDK II UEFI firmware, found by Alex Matrosov and Dan Holmes-Mitra. It is exploitable only while a machine is PXE network booting and the attacker sends an oversized ICMP error from the same network. Code execution also needs the exact firmware build, and Secure Boot does not help. The fix landed in EDK II main on 15 October but is not in a stable release. No known exploitation, and not in CISA KEV.

EDK IIUEFITianoCore+2
CVE-2026-97631Alex MatrosovDan Holmes-Mitra+3

Hardware & RFΒ· Added 30 Oct 2026, published 28 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-92885 is a critical (CVSS 3.1 9.8, CWE-287) authentication bypass in the Qode Membership WordPress plugin, versions through 2.0.6.2. A misspelled variable in the Facebook token-verification guard skips provider checks, so an unauthenticated attacker with a public nonce can get a session cookie for an existing account, including an administrator. The post gives the fix (2.0.6.3, bundled in Bridge 30.9), KEV/EPSS/SSVC status, and a SOC log-correlation and remediation plan.

WordPressQode MembershipBridge+3
CVE-2026-92885CWE-287Wordfence+4

AppSec, Identity & Access, Blue Team & DetectionΒ· Added 31 Oct 2026, published 28 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

CISA Warns of Node2Shell Exploitation as Honeypots Log Attack Attempts

CVE-2026-111497 (Node2Shell, also HTTP2Shell and Broccoli2Shell) is an out-of-bounds write in the Brotli decoder, affecting versions 1.0.3 through 1.2.0. CISA added it to the KEV catalog on 27 October 2026 with a federal deadline of 10 November. Previdian and ELLIO logged exploitation attempts; ELLIO found the observed exploit broken but achieved code execution itself, and Broadcom's VMware SDDC Manager patches are pending.

BrotliNode.jsVMware Cloud Foundation+2
CVE-2026-111497Node2ShellHTTP2Shell+9

Threat Intel, AppSecΒ· Published and added 28 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA alert of 27 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities (KEV) Catalog on evidence of active exploitation: CVE-2026-48356, an unrestricted upload of a dangerous file type in Adobe Commerce and Magento, and CVE-2026-111497, an unchecked return value in Google Brotli. It restates BOD 26-04, which makes federal civilian agencies prioritise KEV flaws on exposed assets and check for prior compromise. No technical detail or IOCs are given.

Adobe CommerceMagentoBrotli
CVE-2026-48356CVE-2026-111497CISA KEV+2

AppSec, GRCΒ· Added 29 Oct 2026, published 27 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-115905 is a ZIP cloaking flaw in the Rust zip crate (zip-rs/zip2), rated CVSS v4.0 10.0 and affecting versions below 9.0.5. ZipArchive reads central-directory metadata while ZipStreamReader reads local headers, so a crafted archive can pass filename inspection and then overwrite a different file during streaming extraction. Version 9.0.5 adds consistency checks, but ZipStreamReader::new leaves them off by default, and extraction is not atomic, so files can be written before an error is raised. The post covers CWE-20 and CWE-436, KEV and EPSS status, Debian status and a six-step investigation trail.

Rustzip crateCargo+3
CVE-2026-115905CWE-20CWE-436+3

AppSec, Blue Team & DetectionΒ· Added 29 Oct 2026, published 27 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

This is Fine: What NetScaler Zero-Days Tell Us About the New Normal

This SecurityWeek commentary covers the September 2026 Citrix NetScaler ADC and Gateway zero-days, exploited from mid-month and patched on 27 September as unauthenticated RCE flaws CVE-2026-88771 through CVE-2026-88778. The author argues the fast response shows stronger defence. Cited evidence: Citrix disclosure time fell from about 40 days to 17 in 2026 after it set up a NetScaler CNA, and CISA made a rare Sunday KEV addition.

Citrix NetScaler
CVE-2026-88771CVE-2026-88772CVE-2026-88773+9

other, Threat IntelΒ· Published and added 27 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Maritime Coalition Launches Free Vulnerability Database for Ship and Port Systems

Blue Initiative is a free public vulnerability database for maritime IT and OT, built by Cydome, ClassNK, Bureau Veritas, MTS-ISAC and Rakuten Maritime. It holds nearly 30,000 entries, over 2,000 rated critical by CVSS and more than 580 known exploited. Only 37 affect ship and port products. Most entries are pulled from CISA ICS advisories and the KEV catalog and mapped to maritime systems.

CISA KEVCVSS
Blue InitiativeCydomeClassNK+5

otherΒ· Published and added 27 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA added two PHP vulnerabilities to its Known Exploited Vulnerabilities Catalog on 26 October 2026: CVE-2026-109618 (memory corruption) and CVE-2026-109619 (stale internal request state). It also updated its PHP alert on critical vulnerabilities requiring immediate patching. The alert restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise.

PHPCISA KEV
CVE-2026-109618CVE-2026-109619BOD 26-04+1

AppSec, GRCΒ· Added 29 Oct 2026, published 26 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

PHP2Shell Exploitation Moves From Probes to Working Shells

PHP2Shell exploitation (CVE-2026-109618, CVE-2026-109619) reached working shells on 24 October 2026, when Perplexity researcher Adel Karimi's honeypots (PHP 8.4.26, Apache mod_php, single worker) logged 35 shells across three servers. Attackers used a four-stage HTTP chain: memory exhaustion, memory leak, then shell command execution, matching a public PoC. No second-stage payload was seen, and CISA had not added the flaws to KEV as of 26 October.

PHPApache
CVE-2026-109618CVE-2026-109619PHP2Shell+4

Threat Intel, AppSecΒ· Published and added 26 Oct 2026

x.comarticleπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge CVE of the Day #087 covers CVE-2026-115889, a Cranelift value-index overflow in Wasmtime that can miscompile crafted WebAssembly and possibly escape the sandbox (CVSS 9.9, CWE-197 and CWE-843). Affected: below 36.0.19, and 37.0.0 up to but excluding 43.0.0; fixes are 36.0.19 and 43.0.0. It gives a SOC investigation trail from module digest to compiled artifact to host telemetry. EPSS is 0.454%, with no KEV entry.

WasmtimeCraneliftWebAssembly+4
CVE-2026-115889GHSA-897f-g5gm-fmxmRUSTSEC-2026-0380+5

AppSec, Blue Team & DetectionΒ· Added 28 Oct 2026, published 26 Oct 2026

x.comarticleπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge Weekly CVE Rundown #007 covers six CVEs from 19 to 24 October 2026: SiteGuard command injection (CVE-2026-106931), DB-GPT (CVE-2026-77932), Siemens Software Center DLL side-loading (CVE-2026-110936), Cisco Expressway (CVE-2026-76466), Node.js Brotli (CVE-2026-111497) and Arista VeloCloud (CVE-2026-114625). Each entry gives defender actions, fixed versions, exploitation status and primary-source links. Updated 25 October 2026 with CISA KEV and EPSS findings.

SiteGuardDB-GPTSiemens Software Center+4
CVE-2026-106931CVE-2026-77932CVE-2026-110936+10

Blue Team & Detection, AppSec, Threat IntelΒ· Added 27 Oct 2026, published 25 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-111497 is an out-of-bounds write in the Brotli decoder bundled with Node.js (CWE-787, CWE-252), rated CVSS v4.0 9.2 by the Google CNA and High by the Node.js project. Fixes are Node 22.23.4, 24.22.1 and 26.12.1, and 24.22.1 still labels Brotli 1.2.0 because the fix was cherry-picked. The post gives a SOC trail from input to worker, with remediation and verification steps. It notes no KEV match, CISA SSVC exploitation none, and only unverified public lab claims.

Node.jsBrotliCVSS+3
CVE-2026-111497CWE-787CWE-252+3

Blue Team & Detection, AppSecΒ· Added 26 Oct 2026, published 23 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge CVE of the Day #084 analyses CVE-2026-76466, a CVSS 9.8 flaw in clustered Cisco Expressway-C and Expressway-E. Persistent database cookies and weak client-certificate validation allow root OS command execution over the network. The fix is X15.5.20 (X14 and earlier must migrate), with no workaround. It adds a per-peer SOC investigation trail, reachability checks and exposure status from CISA SSVC, KEV and EPSS.

Cisco ExpresswayCVSSNVD+2
CVE-2026-76466CWE-798cisco-sa-vcs-static-cred-hr7EWZ8t+2

Blue Team & Detection, Cloud & InfraΒ· Added 24 Oct 2026, published 22 Oct 2026

x.comarticleπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-110936 is an uncontrolled DLL search path flaw (CWE-427) in Siemens Software Center below V4.0.9.8, listed in CISA KEV on 20 October 2026. The post covers CVSS v4.0 8.4 and v3.1 6.7, Siemens' Romulus ClickFix campaign indicators (IPs, domain, hashes, file leads) and a six-step SOC trail using Sysmon, EDR and network records. It separates delivery from DLL load and from compromise.

Siemens Software CenterWindowsSysmon+3
CVE-2026-110936CWE-427DLL search order hijacking+10

Blue Team & Detection, Threat IntelΒ· Added 24 Oct 2026, published 21 Oct 2026

unit42.paloaltonetworks.comadvisoryπŸ›‘οΈ Security

Threat Brief: Active Exploitation of PAN-OS CVE-2026-0257 (Updated Oct 20)

Unit 42 threat brief on active exploitation of CVE-2026-0257, a PAN-OS GlobalProtect authentication bypass added to CISA KEV on May 13, 2026. It lists IP addresses, host IDs and PoC-derived client values to hunt in GlobalProtect logs. The October 2026 updates cover Qilin and Inc ransomware operators, MFA bypass, pivots to vCenter and ESXi with offline VMDK credential dumping, and management interface exposure on ports 4443 and 3879.

PAN-OSGlobalProtectVPN+3
CVE-2026-0257CVE-2023-27532Spikey Scorpius+10

Threat Intel, Blue Team & Detection, Identity & AccessΒ· Added 21 Oct 2026, published 20 Oct 2026

blog.talosintelligence.comarticleπŸ›‘οΈ Security

There's only so much code: the rise in vulnerability numbers

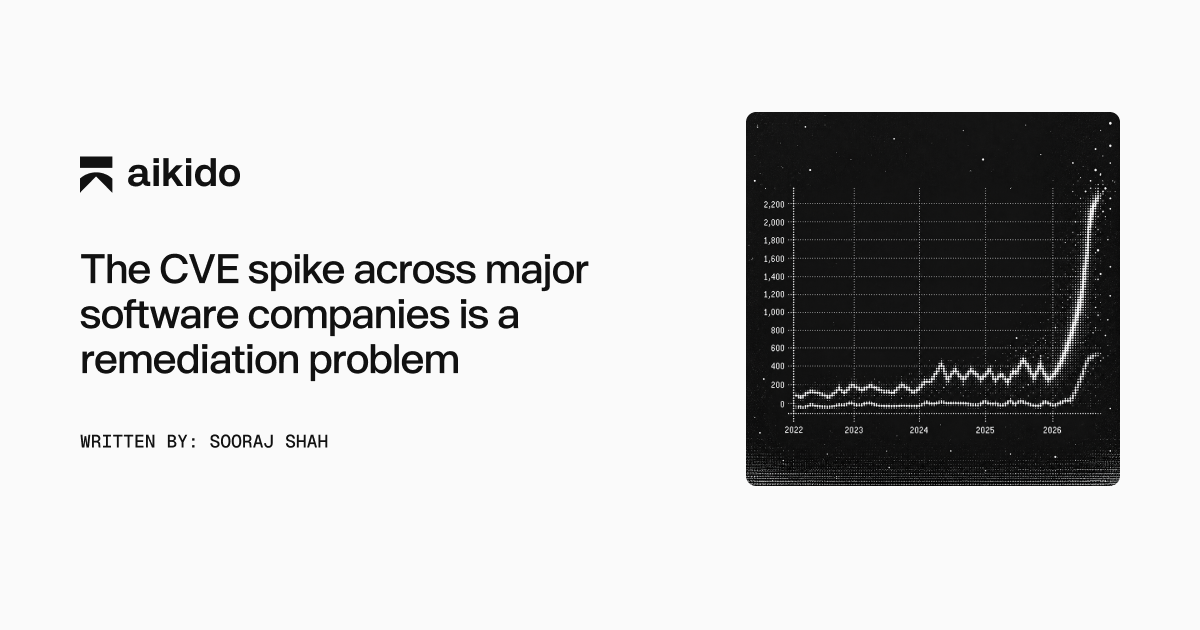
Cisco Talos analysis of why Microsoft Patch Tuesday advisories rose from about 100 a month before June 2026 to 975 in September and 1,415 in October, as frontier models such as Mythos mine old code. CVEs grew 105% year over year while CISA KEV additions grew 37%, and only three September advisories were exploited in the wild. It covers pressure on 90-day coordinated disclosure and open-source maintainers, the format string bug-class precedent, and defender advice.

SnortWindows
CVE-2021-44228MythosCISA KEV+8

AI Security, AppSec, Blue Team & DetectionΒ· Published and added 20 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-77932 affects DB-GPT through 0.8.2 (dbgpt-app). The /api/v1/chat/react-agent route accepts unauthenticated requests because get_user_from_headers returns an admin-role user, and the ReAct agent can reach unsandboxed Python and shell tools. Lasso reported root in the webserver container in a lab. The post gives CVSS 9.8 and 9.3, no verified fix (0.8.2 is still the latest release), no KEV match, no EPSS data, and a SOC hunting trail.

DB-GPTPythonDocker+3
CVE-2026-77932CWE-306Lasso+4

AI Security, AppSec, Blue Team & DetectionΒ· Added 23 Oct 2026, published 20 Oct 2026
securityweek.comarticleπŸ›‘οΈ Security

Exploited Fortinet Bug Linked to Stealthy FortiGate Implant in Telecom Hack

UNC5820 (tracked by Palo Alto Networks as CL-STA-0954) breached a telecom in September 2024 using FortiManager flaw CVE-2024-47575 (FortiJump) and path traversal CVE-2025-61624, then deployed PeerStitch, a memory-resident ARM64 FortiGate implant. PeerStitch patches FortiOS log and IKE/IPsec daemons to build a covert bridge without listening ports. The actor also impersonated FortiManager over FGFM, using CVE-2024-26008. CISA added CVE-2025-61624 to KEV.

FortiGateFortiManagerFortiOS+1
CVE-2024-47575CVE-2025-61624CVE-2024-26008+8

Threat Intel, Malware & REΒ· Published and added 19 Oct 2026

x.comrepo🧠 AI

Saylor (@Kev96790724) on X

G-Krusch is an MIT-licensed, local-first Google Workspace hub built on Node.js 22 and SQLite WAL. It runs a 12-tool MCP server (SSE and Stdio) plus a REST bridge on port 5446 for Drive, Calendar and Gmail. It includes a 1,024-dimension hybrid Drive RAG with an embedding cascade (Ollama bge-large, then Gemini, then offline fallback) and FTS5 BM25. PDF extraction returns page citations. Tokens are kept in an AES-256-GCM vault; 30 of 30 tests pass.

Model Context ProtocolNode.jsSQLite+5
G-KruschKrusch CompanionKruschNexus+1

mcp, llm-apps, coding-agentsΒ· Added 21 Oct 2026, published 19 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

Plex2Shell is a chain of four Plex Media Server flaws (CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656) that a researcher says ends in unauthenticated RCE on servers older than 1.43.3.10861. A write-up and PoC were published on 16 October 2026. CISA advisory VA-26-266-01 scores the individual CVEs 4.3 to 7.2, and they are not in CISA KEV. The post advises updating, avoiding exposure of port 32400, and checking for unknown child processes and new files in the Codecs folder.

Plex Media ServerDocker
CVE-2026-96652CVE-2026-96654CVE-2026-96655+6

AppSec, Offensive SecurityΒ· Added 19 Oct 2026, published 18 Oct 2026

x.comarticleπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge Weekly CVE Rundown #006 covers six CVEs from 12-17 October 2026: BotSharp default signing key, GitLab CI/CD regex compiler overflow (CVSS v3.1 10.0), Ivanti Connect Secure auth bypass, Cisco Secure Email Gateway, BeyondTrust Remote Support and the Linux kernel PwnEscape guest-to-host bug. It gives fixed versions, KEV and EPSS status as of 18 October, and separates patch verification from compromise investigation.

GitLabIvanti Connect SecureCisco Secure Email Gateway+3
CVE-2026-108860CVE-2026-97229CVE-2026-104935+9

Blue Team & Detection, Threat IntelΒ· Added 20 Oct 2026, published 18 Oct 2026
x.comthreadπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

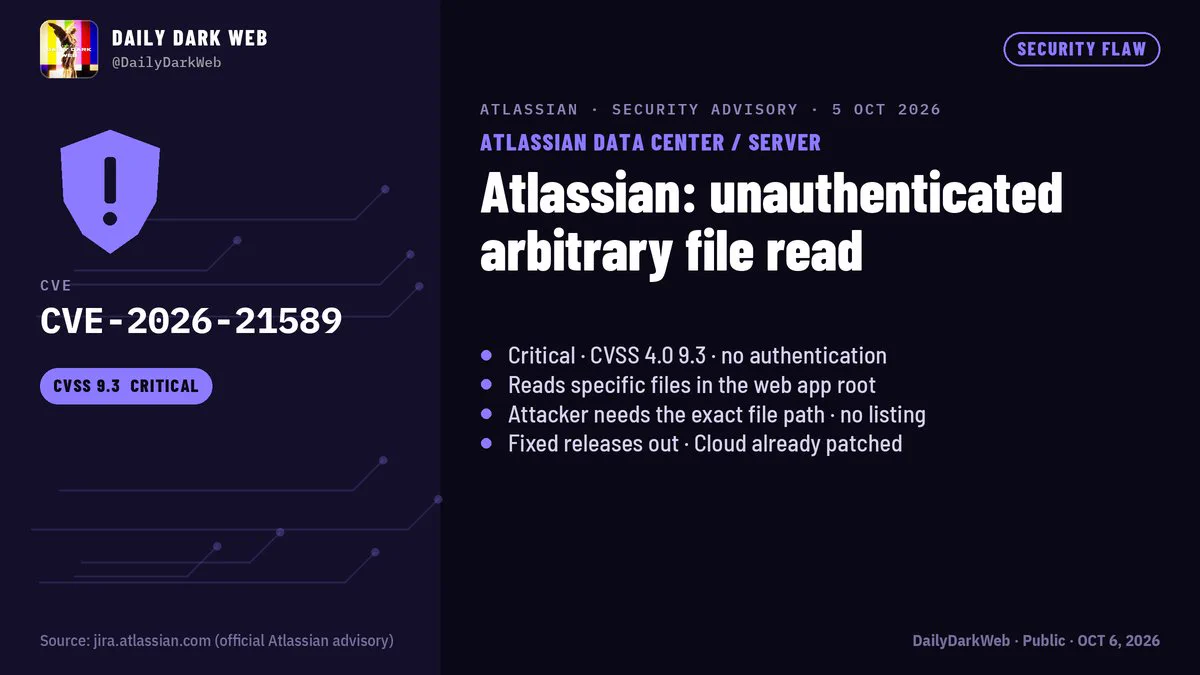
DailyDarkWeb update on CVE-2026-21589, a pre-auth file-read flaw in Atlassian Data Center products. The CVE record was rejected on 16 October 2026 with a generic reason and no replacement ID, but Atlassian's advisory (CVSS v4.0 9.3, Critical) and the CISA KEV listing (added 15 October, federal due date 18 October) remain. The analyst note says to keep patching to the fixed versions and track versions, not only the CVE ID.

JiraConfluenceCVSS+1
CVE-2026-21589CISApre-auth file read+1

Threat Intel, AppSecΒ· Added 19 Oct 2026, published 18 Oct 2026
watchtowr.comadvisoryπŸ›‘οΈ Security

Frequently Asked Questions About the BeyondTrust Remote Support Arbitrary File Upload (CVE-2026-102764)

CVE-2026-102764 is an arbitrary file upload in BeyondTrust Remote Support (formerly Bomgar) caused by internal appliance components not validating message origin. Mandiant found it exploited as a zero-day in late August 2026. BeyondTrust disclosed it on 15 October 2026 and CISA added it to KEV on 16 October 2026. The FAQ covers the web shell, root escalation, credential theft, persistence, patching and compromise checks.

BeyondTrust Remote Support
CVE-2026-102764CISA KEVMandiant+4

AppSec, Threat IntelΒ· Added 30 Oct 2026, published 16 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

I Want to Ride My BIKE: Customizing Bit-Flipping Decoders for Ephemeral Key KEMs

ePrint paper presenting the first optimized implementation of the BF-max bit-flipping decoder for the code-based KEM BIKE, combined with other decoders to trade off decoding failure rate, runtime, public-key and ciphertext size in ephemeral-key settings. It cuts public-key and ciphertext sizes by 7.8% versus LeanBIKE at similar speed and DFR, and gives a combined size 22% below BIKE and 2.79x below HQC. It shows BIKE can fit constrained protocols such as IKEv2, which matters for practical post-quantum migration.

BIKEHQCIKEv2
BF-maxLeanBIKEQC-MDPC+1

otherΒ· Added 17 Oct 2026, published 16 Oct 2026

watchtowr.comadvisoryπŸ›‘οΈ Security

BeyondTrust Remote Support Arbitrary File Upload (CVE-2026-102764)

CVE-2026-102764 is a CVSS 9.8 unauthenticated arbitrary file upload flaw in BeyondTrust Remote Support (formerly Bomgar) and Privileged Remote Access. Internal messaging components do not verify message origin, so remote attackers can plant files the appliance would reject. BeyondTrust disclosed it on 15 October 2026 with patch BT26-05, and CISA added it to KEV on 16 October 2026. The page lists log files to review and hardening steps.

BeyondTrust Remote SupportBeyondTrust Privileged Remote AccessCVSS
CVE-2026-102764BT26-05CISA KEV+2

AppSec, Blue Team & DetectionΒ· Added 30 Oct 2026, published 16 Oct 2026

x.comthreadπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge "CVE of the Day #079" on CVE-2026-102764, a CWE-290 origin-validation flaw in BeyondTrust Remote Support (advisory BT26-05, CVSS v4 9.3) that allows appliance file operations. It summarises Mandiant/GTIG's exploited intrusion chain (SAWFLY web shell, BARECLAW backdoor, root escalation, persistence) and gives an investigation trail: patch-state verification (BT26-05-RS), evidence preservation, hunting leads with SHA-256 hashes and YARA rules, permission/session correlation, and remediation including clean redeployment and credential rotation. It separates vendor facts from the intrusion's observed behaviour and notes that KEV and EPSS have no entries.

BeyondTrust Remote SupportYARASIEM+2
CVE-2026-102764BT26-05CWE-290+7

Blue Team & Detection, Threat IntelΒ· Added 18 Oct 2026, published 16 Oct 2026

blog.talosintelligence.comarticleπŸ›‘οΈ Security

The Q3 Vulnerability Pulse: Discovery β‰  Exploitation

Talos Threat Source newsletter arguing that record CVE volume (over 70k by end of Q3, six-digit CVE IDs) is not the same as exploitation. KEV grew only 37% YoY against 105% for CVEs, about a third of KEV entries are CVEs from 2025 or earlier (a patch gap), and 29% of 2026 KEV CVEs were added on their publication date. It also notes the new KEV "forensicTriage" column (BOD 26-04), summarizes the Talos/Insikt report on UAT-6275 espionage against CIS governments with GitHub-hosted payloads and a WinRAR exploit, and lists weekly headlines.

CISA KEVGitHubPowerShell+2
CVE-2026-104935CVE-2014-125110CVE-2015-1000013+7

Threat Intel, otherΒ· Published and added 15 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

Daily CVE digest on CVE-2026-76519, a CVSS 9.8 relative path traversal (CWE-23) in Cisco Secure Email Gateway's AMP File Reputation attachment processing. A crafted attachment gives unauthenticated arbitrary file writes and root command execution, and Cisco PSIRT reports active exploitation. The CVE is in CISA KEV. It lists the applicability conditions (File Reputation assigned to a policy and Content Scanner Tools earlier than 25.3.0.5525) and the fixes (scanner 25.3.0.5525, AsyncOS 15.5.5-014 and 16.5.0-780). It also covers evidence preservation, reading Cisco's System Security scan outcomes, mail/AMP log correlation, and deployment-specific recovery including cluster-key exposure.

Cisco Secure Email GatewayCisco AsyncOSCVSS+2
CVE-2026-76519CWE-23CISA KEV+4

Blue Team & Detection, Threat IntelΒ· Added 18 Oct 2026, published 15 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Palo Alto Networks Patches PAN-OS Zero-Day Exploited for Remote Code Execution

Palo Alto Networks patched CVE-2026-0322, a high-severity zero-day in the PAN-OS management interface that lets an authenticated attacker with network access run arbitrary code as root. It affects PA-Series, VM-Series and Panorama with no special configuration needed, and "very limited" exploitation has been seen. The vendor published a few IP-based IoCs, CISA added the flaw to KEV with an October 17 deadline, and a dozen other medium/low advisories were released the same day.

PAN-OSPalo Alto NetworksPanorama+1
CVE-2026-0322CISA KEVCISA

Threat Intel, Cloud & InfraΒ· Published and added 15 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Cisco Warns of Exploited Secure Email Gateway Vulnerability

Cisco warned that CVE-2026-76519 (CVSS 9.8), an unauthenticated arbitrary file write in the Advanced Malware Protection feature of Secure Email Gateway, is exploited in the wild. Crafted email attachments can lead to root command execution when file reputation is enabled and Content Scanner Tools is older than 25.3.0.5525. Fixes shipped September 14 in AsyncOS 15.5.5-014 and 16.5.0-780. Cisco published IoCs, advises rebuilding virtual appliances and rotating credentials, and CISA added the flaw to KEV. It is the second exploited SEG bug since mid-September, after CVE-2026-76461.

Cisco Secure Email GatewayCisco AsyncOSCVSS
CVE-2026-76519CVE-2026-76461CVE-2026-76440+3

Threat Intel, Blue Team & DetectionΒ· Published and added 15 Oct 2026

orca.securityadvisoryπŸ›‘οΈ Security

Critical GitLab RCE Lets Unauthenticated Attackers Execute Code on Servers (CVE-2026-97229)

Orca Security analysis of CVE-2026-97229, a CVSS 10.0 flaw in GitLab CE/EE. An integer overflow (CWE-190) in the CI/CD regular expression compiler gives memory corruption and code execution as the git user. It is triggered by a crafted regex in .gitlab-ci.yml combined with a UTF-8 repository path, with no authentication needed on instances that allow public project creation or self-registration. Lists affected branches (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2), the absence of a workaround, interim mitigations, and a Rapid7 PoC against GitLab CE 19.4.1 with ASLR on. Notes a prior max-severity GitLab bug (CVE-2026-85706) was probed in the wild within hours and later added to CISA KEV.

GitLab
CVE-2026-97229CVE-2026-85706CWE-190+2

AppSec, DevSecOpsΒ· Published and added 14 Oct 2026

x.comthreadπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

Defender guide for CVE-2026-104935, an authentication-bypass-by-spoofing flaw (CWE-290) in Ivanti Connect Secure that allows unauthenticated command execution. It is confirmed exploited and CISA KEV-listed, with a CNA CVSS 8.6. It covers the fixed-release matrix (25.1.1.2, 22.8R2.5, 25.1.3.x), platform and cluster migration limits, and Volexity's UTA0576 indicators and YARA rules. It also gives a six-step SOC workflow (scope, preserve, hunt, correlate identity, remediate, verify). It stresses that a clean ICT result cannot clear memory-only activity and that LDAP, LAPS and BitLocker exposure belongs to one observed chain.

Ivanti Connect SecureVPNYARA+3
CVE-2026-104935CWE-290UTA0576+6

Blue Team & Detection, Threat IntelΒ· Added 16 Oct 2026, published 14 Oct 2026

x.comthreadπŸ›‘οΈ Security

ThreatWire (@ThreatWire_) on X

ThreatWire post on CVE-2026-97229, an integer overflow in the GitLab CI/CD regex compiler. GitLab rates it CVSS 3.1 10.0 and says it can allow unauthenticated code execution under certain conditions, in both CE and EE. Fixes are in 19.2.8, 19.3.5 and 19.4.2 (not 19.3.4), released Oct 12; GitLab-hosted instances are already patched. The post credits joaxcar via HackerOne and says a Rapid7 researcher published a lab PoC on GitHub, which ThreatWire has not run or verified. It also says the CVE is not in CISA KEV and has no known exploitation.

GitLab
CVE-2026-97229integer overflowjoaxcar+1

AppSecΒ· Added 15 Oct 2026, published 14 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Microsoft Patches Record 1,413 Vulnerabilities, Including Exploited Windows Zero-Day

SecurityWeek reports Microsoft's October 2026 Patch Tuesday fixed a record 1,413 CVEs (1,102 in Windows, 134 Office, 36 SharePoint), more than all of 2025, with the surge attributed largely to AI-driven discovery. The exploited zero-day CVE-2026-96951 is a Windows shell Mark of the Web security feature bypass (CVSS 8.8), added to CISA KEV with an October 16 deadline. Two flaws were publicly disclosed: CVE-2026-108398 (WDAC bypass) and CVE-2026-92707 (MessagePack-CSharp DoS), and Microsoft introduced 'risk cohorts' for patch prioritization.

WindowsWindows Defender.NET+2
CVE-2026-96951CVE-2026-108398CVE-2026-92707+5

Threat Intel, Blue Team & DetectionΒ· Published and added 14 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

Summary of SAP's October 13, 2026 Security Patch Day (16 new notes, 4 GitHub advisories). It leads with CVE-2026-89111, a CVSS 10.0 OAuth2 SSRF in SAP Cloud SDK for Python before 0.45.2, where an attacker-controlled tenant_subdomain redirects token requests and exfiltrates client credentials. It also lists three other critical flaws: broken access control in NetWeaver Visual Composer, code injection in S/4HANA substitution/validation rules, and a missing authorization check in the Manufacturing Integration and Intelligence (XMII) Configuration Service. It notes that none are in CISA KEV and SAP reports no in-the-wild exploitation.

SAP Cloud SDK for PythonSAP NetWeaverSAP S/4HANA+3
CVE-2026-89111CVE-2026-89110CVE-2026-89107+5

AppSec, Identity & AccessΒ· Added 15 Oct 2026, published 13 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

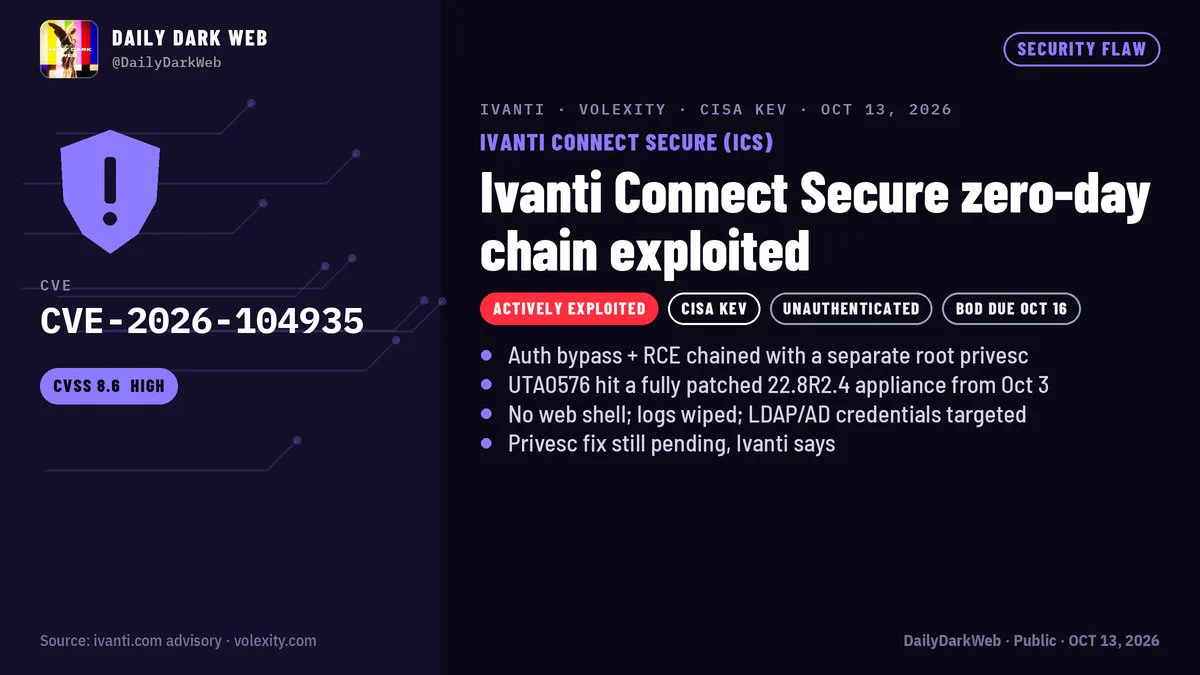
Social post summarizing Volexity's research on an Ivanti Connect Secure (ICS) zero-day chain, CVE-2026-104935. The chain pairs an auth bypass and a race-condition RCE with a separate privilege-escalation bug for root. Actor UTA0576 used it from Oct 3, 2026 against a fully patched 22.8R2.4 appliance, leaving no backdoor or web shell and deleting log entries. Post-exploitation included LDAP/AD credential theft, LAPS and BitLocker key searches, password spraying and packet capture. CISA added it to KEV with a due date of Oct 16. A clean Integrity Checker result does not rule out compromise because the chain patches code in memory only, so memory and network forensics are needed. The hunting lead is heavy requests to /dana-na/auth/url_default/welcome.cgi with a mismatched X-DSCGI-PATH header.

Ivanti Connect SecureVPNActive Directory+1
CVE-2026-104935UTA0576Volexity+5

Threat Intel, Blue Team & DetectionΒ· Published and added 13 Oct 2026

rapid7.comadvisoryπŸ›‘οΈ Security

Ivanti Connect Secure zero-day exploited in the wild (CVE-2026-104935)

Rapid7 emergency-response analysis of CVE-2026-104935, a CVSS 8.6 authentication bypass by spoofing (CWE-290) in Ivanti Connect Secure that allows unauthenticated remote command execution. It was exploited as a zero-day against a limited number of customers, added to CISA KEV on disclosure day, and Volexity observed it chained with a still-unpatched privilege escalation flaw. Part of the fix shipped in 25.1.3.0 in July 2026, with backports to other supported versions pending. Rapid7 advises emergency patching outside normal cycles and hunting for compromise using Volexity's IOCs, since Ivanti has no reliable ones.

Ivanti Connect SecureVPNCVSS
CVE-2026-104935CWE-290CISA KEV+3

Threat Intel, Blue Team & DetectionΒ· Published and added 13 Oct 2026

watchtowr.comadvisoryπŸ›‘οΈ Security

Frequently Asked Questions About the Ivanti Connect Secure Authentication Bypass by Spoofing (CVE-2026-104935)

CVE-2026-104935 is an authentication bypass by spoofing in Ivanti Connect Secure. A remote attacker can forge identity signals and run arbitrary commands without credentials. CISA added it to the KEV catalog on 13 October 2026. The FAQ lists affected branches by ISA hardware (25.1.1.1, 25.1.2.2, 22.8.X), fixed versions (25.1.1.2, 25.1.3.0/25.1.3.1, 22.8R2.5), no workaround and no reliable IOCs.

Ivanti Connect SecureVPN
CVE-2026-104935CISA KEVCISA+1

Threat Intel, Blue Team & DetectionΒ· Added 30 Oct 2026, published 13 Oct 2026

watchtowr.comadvisoryπŸ›‘οΈ Security

Ivanti Connect Secure Authentication Bypass by Spoofing (CVE-2026-104935)

CVE-2026-104935 is an authentication bypass by spoofing in Ivanti Connect Secure (CVSS 3.1 score 8.6) that lets a remote attacker run commands without logging in. CISA added it to KEV on 13 October 2026. The 22.8.X bridge release and 25.1.2.2 and earlier are affected, with fixes in 22.8R2.5, 25.1.1.2, 25.1.3.0 and 25.1.3.1. Ivanti says no reliable indicators of compromise exist yet.

Ivanti Connect SecureVPN
CVE-2026-104935CISA KEVVolexity+2

AppSec, Threat IntelΒ· Added 30 Oct 2026, published 13 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge "CVE of the Day #076" covers CVE-2026-97229, a CVSS 10.0 integer overflow (CWE-190) in GitLab CE/EE's CI/CD regular expression compiler. It can lead to conditional unauthenticated code execution on the GitLab server. It lists the affected trains (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2) and the 19.3.4 vs 19.3.5 Ona-regression discrepancy. It also gives six SOC checks: scoping, log preservation (Workhorse/Rails/Sidekiq, correlation_id), server-effect hunting, request-to-process correlation, upgrade and running-state verification. It notes that exploit details are unverified, no KEV listing exists and EPSS data is unavailable.

GitLabCVSSEPSS+2
CVE-2026-97229CWE-190CISA KEV+3

AppSec, Blue Team & DetectionΒ· Added 15 Oct 2026, published 13 Oct 2026

becomingahacker.orgarticle🧠 AI

AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples

Guided tour of Omar Santos's eight-part AI-agents-for-cybersecurity repository. It moves from LLM building blocks (LangChain, RAG) to security agents built with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan). It also covers a hardening guide for six agentic frameworks, token-cost control, and a spec for a supervisor-led, human-gated assessment harness. Design lessons include least-privilege subagents, single-use approvals and kill switches.

LangChainRAGLangGraph+7
Omar SantosOWASPCISA+1

agents, mcp, llm-appsΒ· Added 13 Oct 2026

github.comrepo🧠 AI

santosomar/AI-agents-for-cybersecurity

Companion repository for Omar Santos's Pearson and O'Reilly trainings and books. It has eight parts of runnable Python labs: chat models, embeddings, prompt templates, LCEL prompt chaining, Chroma-based RAG, ReAct/LangGraph/CrewAI/DeepAgents agents, and FastMCP servers (nmap, CISA KEV, Shodan). It also includes guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz), a tokenomics module on agent cost (context compounding, prompt caching, model routing, token budget guards, batch API, cost per accepted outcome), and a vendor-neutral design spec for a human-gated multi-agent assessment harness. It is a current, practical curriculum for building and operating agents. Some examples act on real systems and should only be run in an authorized lab.

PythonuvLangChain+17
Omar SantosPearsonO'Reilly+15

agents, llm-apps, mcpΒ· Added 13 Oct 2026

github.comrepoπŸ›‘οΈ Security

santosomar/AI-agents-for-cybersecurity

Omar Santos's companion repo for his Pearson/O'Reilly trainings and books, organised in eight parts. They cover LangChain prompts, chains and RAG (Chroma), and agents (LangGraph, CrewAI, DeepAgents). They also cover FastMCP security servers (nmap, CISA KEV, Shodan) and attack-surface-management and SOC agent examples. Later parts have security guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz) with hardening notes and 2026 CVE mapping, agent cost/tokenomics scripts including denial-of-wallet budget guards, and a vendor-neutral spec for a human-gated multi-agent security-assessment harness (scope manifest, approval gates, kill switch). Useful as a hands-on path into AI-agent security tooling, with warnings that some examples act on real systems.

Model Context ProtocolLangChainOpenClaw+3
Omar SantosSSRFCISA KEV+2

AI Security, LearningΒ· Added 13 Oct 2026

becomingahacker.orgarticleπŸ›‘οΈ Security

AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples

Omar Santos walks through his eight-part AI-agents-for-cybersecurity repository: LLM building blocks (LangChain, RAG), then security agents with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan), a hardening guide for six agentic frameworks, token-cost control for agents, and a spec for a supervisor-led, human-gated security-assessment harness. It covers concrete design lessons such as least-privilege subagents, staged response actions, single-use approvals bound to exact actions, kill switches, and mapping controls to the OWASP Top 10 for Agentic Applications. Also notes Project CodeGuard rules shipped for AI coding assistants.

LangChainModel Context ProtocolPython+3
Omar SantosProject CodeGuardOWASP Top 10 for Agentic Applications+5

AI Security, Learning, Blue Team & DetectionΒ· Added 13 Oct 2026

linkedin.comarticleπŸ›‘οΈ Security

AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples

Omar Santos walks through his AI-agents-for-cybersecurity GitHub repo, which has eight parts. Parts 1–4 cover LLM basics (LangChain, prompting, LCEL, RAG). Parts 5–8 cover building security agents with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan), and a hardening baseline for six ready-made agentic frameworks. They also cover token-cost control (caching, routing, budget guards, cost per accepted outcome) and a supervisor-led, human-gated security-assessment harness spec with single-use approvals, a kill switch and an append-only audit log. The post also covers Project CodeGuard rules for AI coding assistants. It is a practical learning path and a reference for governing and securing agents.

LangChainLangGraphCrewAI+5
Omar SantosProject CodeGuardOWASP Top 10 for Agentic Applications+9

AI Security, Learning, Blue Team & DetectionΒ· Added 13 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge's CVE of the Day #075 covers CVE-2026-108860, a critical (CVSS 9.1 v3.1 / 9.3 v4.0) authentication bypass in SciSharp BotSharp through 5.2.0. WebStarter ships a published default HMAC JWT signing secret (CWE-321), so anyone holding it can forge bearer tokens that impersonate known users, including administrators. The post sets out how to confirm the effective key and serving build, a six-step SOC investigation trail, and remediation by rotating the secret. No verified fixed release, KEV entry or EPSS data existed at cutoff, and the linked research is static-only.

BotSharpASP.NET CoreJWT+5
CVE-2026-108860CWE-321VulnCheck+2

AppSec, Identity & Access, Blue Team & DetectionΒ· Added 13 Oct 2026, published 12 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Critical SonicWall Vulnerability Exploited Days After Disclosure

SecurityWeek reports that CVE-2026-102255, a CVSS 10 pre-authenticated SSRF in the SonicWall SMA1000 Work Place interface, was exploited within days of its October 6 disclosure. Defused saw the first attempts on its SMA decoys on October 8, and Previdian (formerly KEVIntel) also observed exploitation. SonicWall urges 6210, 7210 and 8200v customers to update to 12.5.0-03082 or 12.4.3-03670, and Horizon3.ai warns that exploitation could lead to device takeover.

SonicWallCVSS
CVE-2026-102255SSRFCWE-918+4

Threat Intel, AppSecΒ· Published and added 12 Oct 2026

x.comthreadπŸ›‘οΈ Security

ThreatWire (@ThreatWire_) on X

Post announcing a public PoC for CVE-2026-13043, a critical flaw (CVSS 4.0 9.3, scored by WatchGuard) in PSKMAD, the kernel memory access driver of WatchGuard Endpoint Security on Windows. The access-control handshake can be bypassed (CWE-306/CWE-798), letting a local authenticated attacker send privileged commands and read kernel and other processes' memory. Fixed in 8.00.26.0012; the PoC author and LOLDrivers frame the signed driver as BYOVD material, which WatchGuard does not say. The post notes it is not in CISA KEV, has no reported in-the-wild exploitation, and that ThreatWire has not run the PoC.

WatchGuard Endpoint SecurityWindowsCVSS
CVE-2026-13043PSKMADCWE-306+5

Offensive Security, Blue Team & DetectionΒ· Added 11 Oct 2026, published 10 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge CVE of the Day #074 analyses CVE-2026-85097, a CVSS 9.8 unauthenticated file upload to PHP execution flaw (CWE-434) in the Bricksforge WordPress plugin through 3.1.8.9. Wordfence names 3.1.8.10 as the fix, and a separate vendor 4.0.1 Pro Forms upload-security notice has no verified mapping to the CVE. It gives a defender workflow: scope versions, preserve edge/origin logs, inspect resulting files and PHP-FPM handling, and verify the patched version is serving. It also separates KEV (no match), EPSS (0.312%) and SSVC (exploitation none) from compromise evidence.

WordPressPHPCVSS+2
CVE-2026-85097CWE-434Wordfence+4

Blue Team & Detection, AppSecΒ· Added 11 Oct 2026, published 10 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge's CVE of the Day #073 covers CVE-2026-102255, a critical (CVSS 10.0) pre-authentication SSRF / confused-deputy flaw (CWE-918, CWE-441) in the SonicWall SMA1000 Work Place interface, per advisory SNWLID-2026-0017. It lists affected platform hotfixes (12.4.3-03526 and older, 12.5.0-02952 and older), fixed floors (12.4.3-03670, 12.5.0-03082), no workaround, and the exploitation picture (no known exploitation, not in KEV, EPSS 0.477%, SSVC automatable). It gives a six-step SOC playbook covering appliance scoping, AMC log preservation, hunting appliance-originated internal requests, correlating receiving-service changes, patching, and verifying every node, and it separates exposure, a lead, confirmed compromise and telemetry gaps.

SonicWallSMA1000CVSS+3
CVE-2026-102255CVE-2026-102256CVE-2026-102257+7

Blue Team & Detection, AppSecΒ· Added 12 Oct 2026, published 9 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

A Twitter/X post digests joint advisory AA26-281A from FBI, CISA, NSA and allied agencies (UK, Australia, Canada, Japan, New Zealand, Spain) on China-based Integrity Technology Group enabling threat actors, tracked elsewhere as Flax Typhoon, Ethereal Panda and Red Juliett, to target US critical infrastructure, government, healthcare, education and law enforcement networks worldwide. The actors chain open-source scanners, large botnets, XSS, password spraying against Microsoft Exchange, VPN persistence and credential-harvesting scripts. CISA added five exploited CVEs (ISC BIND, Apache Struts, ProFTPD, ONLYOFFICE Docs, Strapi) to its KEV catalog with an Oct 11 federal remediation deadline, and STIX IOCs accompany the advisory.

ISC BINDApache StrutsProFTPD+3
CVE-2015-5477CVE-2016-3081CVE-2015-3306+7

Threat IntelΒ· Published and added 8 Oct 2026

x.comwriteupπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

A detailed "CVE of the Day" thread analyzing CVE-2026-76471, a critical (CVSS 9.8) Cisco advisory covering insufficient NX-API input validation (CWE-122 heap-based buffer overflow) on Nexus 3000/9000 standalone NX-OS and a lower-severity credentialed variant on UCS 6300 Fabric Interconnects via UCS Manager XML API. It compiles Cisco's fixed-software versions per platform, notes the temporary Live Protect shield lp00074, and walks through a six-step SOC evidence-preservation and correlation playbook (scoping affected devices, preserving logs/crash artifacts, reviewing API/shield telemetry, correlating device outcomes, remediating, and verifying post-patch state) while flagging that CISA KEV and FIRST EPSS had no data on the CVE at research time.

CVSSNVDCISA KEV+1
CVE-2026-76471

Cloud & InfraΒ· Published and added 8 Oct 2026

adversa.aiarticleπŸ›‘οΈ Security

Top MCP security resources β€” October 2026

Adversa AI's October 2026 MCP security roundup, aggregating and synthesizing 15 resources: authentication-bypass vulnerabilities in LiteLLM's MCP endpoint (CVE-2026-59822, now CISA KEV), Grafana's MCP server session spoofing/SSRF (CVE-2026-19516), an MCP Python SDK OAuth-fallback flaw exploited by a malicious server returning a 404, and an Obot gateway route-matching bypass reopening GHSA-vw82. It also covers detection failures (two malicious MCP servers passing five scanners including Cisco mcp-scanner and Snyk agent-scan, 12% of 82,000 public MCP configs hardcoding secrets), a malicious npm wallet-signing package (gadgethumans-mcp), the A2M agent-hijacking attack technique, and CoSAI's MCP Security v2.0 governance model.

Model Context ProtocolLiteLLMnpm+3
CVE-2026-59822CVE-2026-59821CVE-2026-19516+6

AI Security, AppSec, Identity & AccessΒ· Published and added 8 Oct 2026

aws.amazon.comarticleπŸ›‘οΈ Security

Configuring your AI vulnerability harness, Part 2: The steering file

AWS Security Blog's second post in a series on building an "AI vulnerability harness" explains the configuration (steering file) that stops an AI model from hallucinating vulnerabilities and inflating severity during security code review. It details five configuration sections β€” structural verification of findings, an evidence-based confidence formula (weighting confirmed taint flow at 0.30), infrastructure-aware severity multipliers for controls like AWS WAF and IAM, CISA KEV/EPSS threat-intel boosting, and a four-tier priority classification β€” and reports validation numbers (e.g., unsteered models fabricated code paths in ~30% of findings; steered confidence of HIGH without structural confirmation was only 34% exploitable vs 89% with confirmed taint). The steering file is shipped as a Kiro steering file, a Kiro skill, and a CLAUDE.md for Claude Code, with full source in a linked GitHub repo.

KiroClaude CodeAWS WAF+3

AI Security, AppSecΒ· Published and added 7 Oct 2026

aws.amazon.comwriteup🧠 AI

Configuring your AI vulnerability harness, Part 2: The steering file

Part 2 of an AWS Security Blog series detailing the design of a "steering file" β€” a persistent instruction set (deployable as a Kiro steering file, Kiro skill, or Claude Code CLAUDE.md) that constrains an LLM performing vulnerability triage. It walks through five configuration sections: requiring structural/dataflow verification before reporting findings, replacing self-reported confidence with a weighted formula based on binary structural signals (e.g., 0.30 weight for confirmed taint flow), mapping infrastructure controls (AWS WAF, IAM) to severity multipliers with a 0.15 floor, incorporating CISA KEV and EPSS threat-intelligence boosts capped at +0.50, and a four-tier priority classification that suppresses low-confidence P3 findings. Validation against a 10-vulnerability test app showed the steered model eliminated fabricated findings and correctly downgraded mitigated vulnerabilities while preserving full severity for a command injection reachable only via authenticated access.

KiroClaude CodeCursor+7
CISAEPSS

prompting, coding-agentsΒ· Added 8 Oct 2026, published 7 Oct 2026

watchtowr.comadvisoryπŸ›‘οΈ Security

Atlassian Jira, Confluence (and more) Arbitrary File Read Vulnerability (CVE-2026-21589)

CVE-2026-21589 is an unauthenticated arbitrary file read (path traversal) in eight Atlassian Data Center and Server products: Bitbucket, Confluence, Jira, Jira Service Management, Bamboo, Crowd, Crucible and Fisheye. Atlassian fixed it on 5 October 2026, and CISA added it to the KEV catalog on 15 October 2026. The page lists patching, WAF regex, Tomcat RewriteValve and urlrewrite.xml mitigations, and a log check for ".." sequences after up to two rounds of URL decoding.

JiraConfluenceBitbucket+3
CVE-2026-21589CISA KEVpath traversal+3

AppSec, Blue Team & DetectionΒ· Added 30 Oct 2026, published 6 Oct 2026

x.comwriteupπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge CVE-of-the-Day #070 on CVE-2026-61500 in Rejetto HFS 3.0.0–3.2.0. The default Koa session-signing key came from Math.random() (CWE-338) and the unauthenticated login handshake leaked outputs of the same generator. That allows recovery of the key, a forged administrator session, and code execution through the legitimate server_code feature. It covers scoring (CVSS 9.8/9.3, EPSS, KEV status), the 3.2.1 fix, a six-step SOC hunting and remediation trail (loginSrp1/2, get_config/set_config pivots, COOKIE_SIGN_KEYS review), and offline jq/Python helpers for container and config metadata.

Rejetto HFSKoaDocker+2
CVE-2026-61500CWE-338VulnCheck+6

Blue Team & Detection, AppSec, Identity & AccessΒ· Added 9 Oct 2026, published 6 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

Atlassian disclosed CVE-2026-21589, a critical (CVSS 9.3) unauthenticated path traversal flaw allowing remote attackers to read specific files within the web application root across its self-managed Data Center/Server products β€” Jira Software, Jira Service Management, Confluence, Bitbucket, Bamboo, Crowd, Crucible, and Fisheye. Fixed versions are listed for each product (e.g. Jira 9.12.40/10.3.26/11.3.12, Confluence 9.2.26/10.2.19), and Atlassian Cloud is already patched; WAF/URL-rewrite mitigations are available for those who can't upgrade immediately. The post's analyst note clarifies exploitation requires knowing the exact target file path (no directory listing), and as of Oct 5, 2026 it is not yet in CISA KEV with no public exploit reported.

JiraConfluenceBitbucket+3
CVE-2026-21589path traversal

AppSecΒ· Added 7 Oct 2026, published 6 Oct 2026

orca.securityadvisoryπŸ›‘οΈ Security

Citrix NetScaler Zero-Day Exploited in the Wild Crashes SAML Authentication Services

Analysis of CVE-2026-88779 (CVSS v4.0 8.7), an unauthenticated memory-overflow flaw in the nsaaad SAML authentication handler on Citrix NetScaler ADC/Gateway that lets attackers crash the SAML service and lock out VPN/SSO access indefinitely through repeated triggering. Affects NetScaler 14.1 before 14.1-73.41 and 13.1 before 13.1-64.28 (plus FIPS/NDcPP builds); watchTowr Labs reproduced it via honeypot activity, Citrix confirmed targeted in-the-wild exploitation from IP 213.209.159.55, and CISA added it to KEV on 2026-10-04 with an Oct 7 federal remediation deadline. Some researchers suspect the overflow could extend to RCE beyond the documented DoS, though Citrix hasn't confirmed this.

Citrix NetScalerSAMLCVSS+1
CVE-2026-88779CWE-119watchTowr Labs+1

Identity & Access, Threat IntelΒ· Published and added 5 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA KEV: Fortinet FortiMail CVE-2026-104286 path traversal, actively exploited, no patch yet

CISA added CVE-2026-104286, a path traversal vulnerability in Fortinet FortiMail, to its Known Exploited Vulnerabilities Catalog on evidence of active exploitation. The alert restates the obligations of BOD 26-04 for Federal Civilian Executive Branch agencies: prioritise KEV CVEs on publicly exposed assets that give total control, and check for compromise before patching. It also describes the KEV nomination criteria: a CVE ID, evidence of exploitation and clear mitigation guidance. The page gives no technical detail, patch status or IOCs.

Fortinet FortiMailCISA KEV
CVE-2026-104286path traversalCISA+1

Threat Intel, GRCΒ· Added 4 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

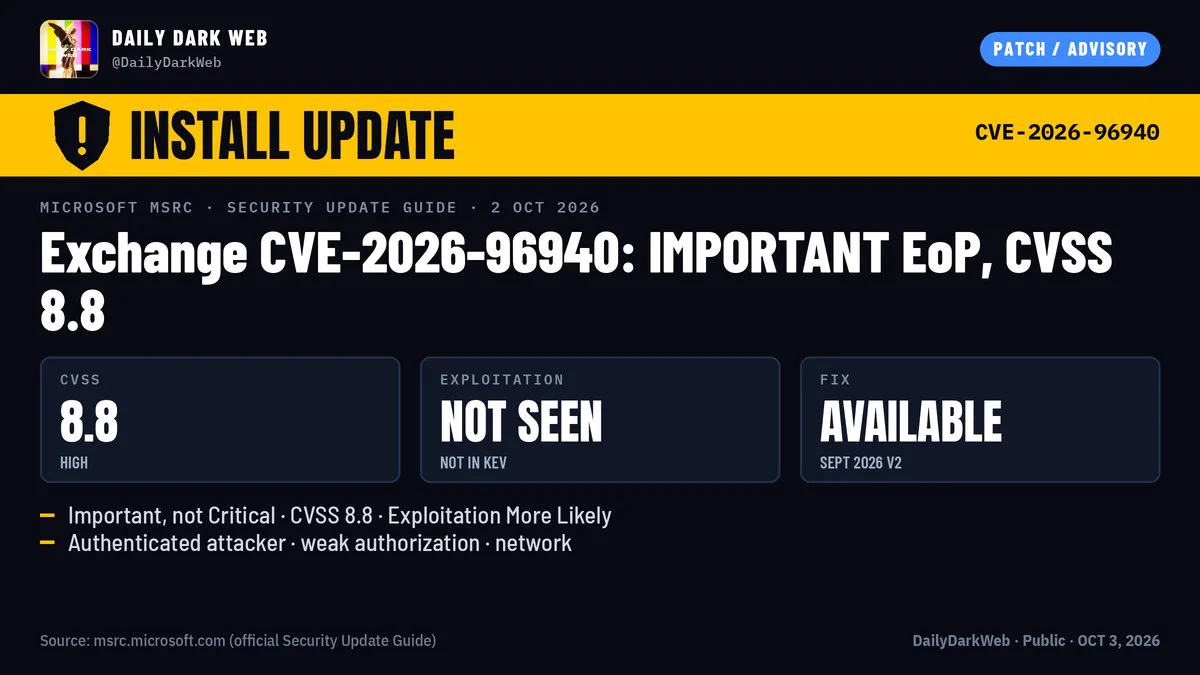
Summary of Microsoft's September 2026 V2 / October 2026 early security updates adding CVE-2026-96940, an Important elevation-of-privilege flaw (CVSS 8.8) in on-prem Exchange Server caused by weak authorization that lets an authenticated attacker escalate privileges over the network. Covers affected builds and KBs (Exchange SE RTM KB5129955, 2019 CU15/CU14 KB5129956/5129957, 2016 CU23 KB5129958) and notes Exchange Online is unaffected, the flaw was found internally by Microsoft with no known exploitation and is not in CISA KEV.

Microsoft ExchangeCVSSCISA KEV
CVE-2026-96940

AppSecΒ· Added 4 Oct 2026, published 3 Oct 2026

decrypt.coarticle🧠 AI

OpenAI Fires Three Safety Researchers Over Alleged Leak to Outside Group

Decrypt reports that OpenAI fired three safety researchers for allegedly sharing confidential information with an outside AI safety organization, per the Wall Street Journal, without naming the people or the recipient group. The piece situates the firings within a pattern of safety-related departures (Ilya Sutskever, Jan Leike, Leopold Aschenbrenner) and a rough stretch of AI-agent incidents β€” a Hugging Face hack, intrusions on U.S. government sites and an Australian Medicare portal β€” that led OpenAI to pause model training twice and introduce an internal misalignment-reporting process.

OpenAIWall Street JournalIlya Sutskever+9

ai-policyΒ· Published and added 1 Oct 2026

rapid7.comadvisoryπŸ›‘οΈ Security

Critical Cisco Catalyst SD-WAN Manager API authentication bypass exploited in the wild (CVE-2026-76504)

Rapid7 analysis of CVE-2026-76504, a critical (CVSSv3.1 9.8) unauthenticated API authentication bypass in Cisco Catalyst SD-WAN Manager caused by improper URL-encoding handling (CWE-177), allowing attackers to gain admin-level API access via crafted requests to the j_security_check endpoint. The flaw is being actively exploited in the wild, was added to CISA's KEV list on October 1, 2026 with a remediation deadline of October 3, and follows two earlier 2026 Catalyst SD-WAN peering authentication bypasses (CVE-2026-20127 and Rapid7-discovered CVE-2026-20182). The post gives fixed-release guidance, no-workaround caveats, and log-based IOCs (encoded-character requests like %6a_security_check, viptela-reserved- usernames) for detecting compromise.

Cisco Catalyst SD-WAN ManagerCVSSCISA KEV
CVE-2026-76504CVE-2026-20127CVE-2026-20182+1

AppSec, Threat IntelΒ· Added 7 Oct 2026, published 30 Sep 2026
x.comthreadπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

A detailed breakdown of CVE-2026-102710 (CVSS v4.0 9.3), a privilege-escalation flaw in Eclipse ThreadX RTOS builds with event tracing enabled: a module-supplied trace callback pointer is retained by the kernel and invoked with kernel privilege when the trace buffer wraps, letting an attacker who already controls a memory-protected user-mode module fault the kernel or execute code in kernel context. The thread walks through the vulnerable code path (registration, storage, invocation across the protection boundary), CWE-269/CWE-822 classification, affected versions (through v6.5.1.202602a_rel), and provides a defender hunting guide plus emergency remediation steps, noting no fixed upstream release or CISA KEV/EPSS entry exists yet.

Eclipse ThreadXCVSSNVD+1
CVE-2026-102710CWE-269CWE-822+1

Hardware & RF, Offensive Security, Blue Team & DetectionΒ· Published and added 30 Sep 2026

orca.securityadvisoryπŸ›‘οΈ Security

Critical Citrix NetScaler Zero-Days Under Active Exploitation

Analysis of two CVSS 9.5 Citrix NetScaler ADC/Gateway zero-days, CVE-2026-88771 (unauthenticated RCE through improper input validation in the management interface, affecting default deployments) and CVE-2026-88772 (memory overflow in DTLS, enabled by default on VPN virtual servers). It lists six more high-severity flaws patched in advisory CTX697096, the affected and fixed versions, and the CISA KEV listing with a federal deadline of 2026-09-30. It advises checking for compromise before patching, since patching can destroy forensic evidence, and gives response steps: isolate, revoke credentials, rebuild firmware, rotate keys and certificates.

Citrix NetScalerVPN
CVE-2026-88771CVE-2026-88772CVE-2026-88773+7

Cloud & Infra, Threat IntelΒ· Published and added 29 Sep 2026
rapid7.comadvisoryπŸ›‘οΈ Security

Zero-Day Exploitation of Citrix NetScaler ADC and Gateway: CVE-2026-88771 and CVE-2026-88772

Rapid7 details active zero-day exploitation of two critical Citrix NetScaler ADC/Gateway RCE vulnerabilities (CVE-2026-88771, CVE-2026-88772, both CVSSv4 9.5), both added to CISA KEV on disclosure day, plus a later SAML denial-of-service zero-day (CVE-2026-88779). The post includes Rapid7 MDR's observed exploitation of CVE-2026-88771 in the wild β€” a command-injection payload that exfiltrates /flash/nsconfig (containing ns.conf admin credentials, SSL private keys, SSH host keys) via the publicly-served /vpn/ path, and a webshell (SHA256 hash provided) found on a compromised appliance β€” along with vendor patch versions and detection guidance.

Citrix NetScalerCVSS
CVE-2026-88771CVE-2026-88772CVE-2026-88779+3

Threat Intel, AppSecΒ· Added 7 Oct 2026, published 28 Sep 2026

watchtowr.comadvisoryπŸ›‘οΈ Security

watchTowr: CVE-2026-88771 Citrix NetScaler ADC/Gateway unauthenticated RCE

watchTowr details CVE-2026-88771 (unauthenticated command execution via improper input validation, affecting every NetScaler ADC/Gateway deployment by default) and CVE-2026-88772 (DTLS memory overflow leading to RCE/DoS, exploitable since DTLS is on by default for VPN virtual servers). Both are confirmed exploited in the wild as zero-days, were pre-notified by NCSC-NL, and CVE-2026-88771 was added to the CISA KEV catalog on September 27, 2026; Citrix's bulletin CTX697096 also fixes six related issues (CVE-2026-88773 through CVE-2026-88778). The writeup gives prioritization guidance, IOC-checking steps, and warns that patching may destroy forensic evidence if done before evidence capture.

Citrix NetScalerCVSSCISA KEV
CVE-2026-88771CVE-2026-88772CVE-2026-88773+8

Threat Intel, Offensive SecurityΒ· Added 5 Oct 2026, published 27 Sep 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA KEV Catalog Additions β€” Check Point, Arista VeloCloud, F5 BIG-IP (Sept 22, 2026)

CISA added four vulnerabilities to the Known Exploited Vulnerabilities catalog on 2026-09-22 based on evidence of active exploitation: two Check Point multi-product flaws (improper certificate validation CVE-2026-85102, path traversal CVE-2026-93616), an Arista VeloCloud Orchestrator improper input validation bug (CVE-2026-93952), and an F5 BIG-IP APM heap-based buffer overflow (CVE-2026-94127). The alert ties the additions to BOD 26-04, which has FCEB agencies prioritize remediation of KEV CVEs on publicly exposed assets that give total control, and to checking for prior compromise before patching.

CISA KEVCheck PointArista VeloCloud Orchestrator+1
CVE-2026-85102CVE-2026-93616CVE-2026-93952+4

Threat Intel, GRCΒ· Added 26 Sep 2026

thehackernews.comadvisoryπŸ›‘οΈ Security

Attackers Exploit WordPress CVE-2026-87902 Within Hours of Patch

CVE-2026-87902 (CVSS 9.2) is an unauthenticated WordPress vulnerability where get_page_template() page-template resolution can be tricked into including an attacker-chosen local .php file outside the active theme directory, leading to RCE when a theme has a page-* top-level directory and a readable local PHP file (e.g. pearcmd.php) exists. Attackers began exploiting it within hours of the September 22, 2026 patch, including pearcmd.php to write PHP web shells to /tmp and /var/tmp and pulling a GitHub-hosted uploader payload, per honeypot telemetry from Previdian and Patchstack with tracked source IPs. CISA added the flaw to its KEV catalog on September 25, 2026, mandating FCEB remediation by September 28; fixed in WordPress 7.1.2, 7.0.6, 6.9.9, and 6.8.10.

WordPressPHPGitHub
CVE-2026-87902CISA KEVpearcmd.php+7

AppSec, Threat IntelΒ· Added 26 Sep 2026

thehackernews.comarticleπŸ›‘οΈ Security

Veeam, Terraform MCP, Django Patch Critical Flaws, Led by CVSS 10.0 Cross-Tenant Bug

The Hacker News roundup covers 11 patched CVEs across three products: Veeam Service Provider Console (CVE-2026-58073, 9.5, unauthenticated managed-agent credential theft; CVE-2026-58072, arbitrary file write to RCE), HashiCorp's Terraform MCP Server (CVE-2026-16498, a 10.0 cross-tenant credential-reuse bug caused by the underlying MCP library not issuing unique session IDs in stateless HTTP mode; CVE-2026-16496 stateful-mode equivalent; CVE-2026-14869 SSRF via header/query-param inconsistency), and Django/GeoDjango (CVE-2026-15307, a spatial-lookup flaw letting GDALRaster write files, reachable by a staff user with view permission on a model with a spatial field, plus a stored XSS, a GEOS DoS, and a language-code DoS). Fixes: Terraform MCP Server 1.1.0+, VSPC 9.3.0.35057, Django 6.0.8/5.2.17; none of the flaws are known to be exploited or listed in CISA KEV as of publication.

TerraformModel Context ProtocolDjango+2
CVE-2026-58073CVE-2026-58072CVE-2026-58067+14

AppSec, AI SecurityΒ· Added 26 Sep 2026

thehackernews.comarticleπŸ›‘οΈ Security

LiteLLM Flaw CVE-2026-42271 Exploited in the Wild, Chains to Unauthenticated RCE

CISA added CVE-2026-42271, a command injection flaw in BerriAI's LiteLLM AI gateway, to its KEV catalog after confirming active exploitation; the bug lets any authenticated proxy user run arbitrary commands via the MCP server test endpoints (/mcp-rest/test/connection and /mcp-rest/test/tools/list), which spawned attacker-supplied stdio subprocess configs. Horizon3.ai separately showed the flaw can be chained with CVE-2026-48710, a Starlette "BadHost" header validation bypass, to skip authentication entirely and achieve unauthenticated RCE (combined CVSS 10.0), exposing model provider credentials and enabling lateral movement into AI infrastructure. Fixed in LiteLLM 1.83.7 (test endpoints now require PROXY_ADMIN role) and Starlette 1.0.1; the article also notes a prior LiteLLM SQLi (CVE-2026-42208) exploited within 36 hours of disclosure.

LiteLLMStarletteModel Context Protocol+1
CVE-2026-42271CVE-2026-48710CVE-2026-42208+4

AI Security, AppSecΒ· Added 26 Sep 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Seven Known Exploited Vulnerabilities to Catalog | CISA

CISA added seven vulnerabilities to its Known Exploited Vulnerabilities Catalog on the basis of active exploitation. They are SQL injection in Sangoma Switchvox, HTTP request/response smuggling in Kludex Starlette, OS command injection in Kestra OSS, improper authentication in BerriAI LiteLLM and JFrog Artifactory, and SSRF plus OS command injection in SonicWall SMA1000 appliances. The alert restates BOD 26-04, which makes federal agencies prioritise rapid remediation of KEV CVEs on publicly exposed assets that grant total control after exploitation. It also requires agencies to check for prior compromise before patching.

Sangoma SwitchvoxStarletteKestra+3
CVE-2026-9586CVE-2026-48710CVE-2026-49869+8

AppSec, GRCΒ· Added 26 Sep 2026

cisa.govotherπŸ›‘οΈ Security

Known Exploited Vulnerabilities Catalog | CISA

CISA's Known Exploited Vulnerabilities (KEV) catalog is the authoritative list of CVEs with confirmed in-the-wild exploitation. It shows 1739 entries, each with vendor, product, description, CWE, ransomware-use flag, date added, due date, and a new BOD 26-04 forensic-triage flag. The latest entries cover Citrix NetScaler, Zammad (chained session fixation and root privilege escalation), Fortinet FortiMail, Cisco Catalyst SD-WAN Manager, WordPress Core, SharePoint, MikroTik RouterOS, Adobe Commerce, WSO2 and Check Point, plus old CVEs such as ProFTPD CVE-2015-3306 and Struts CVE-2016-3081. Feeds are available as CSV and JSON for vulnerability-management prioritisation.

Citrix NetScalerWordPressApache Struts+3
CVE-2015-3306CVE-2021-3199CVE-2023-22894+25

Threat Intel, GRCΒ· Added 26 Sep 2026

arxiv.orgpaper🧠 AI

TrackEverything: Long Horizon Dense Tracking via De-Duplicating 3D Scene Representations

TrackEverything is a 3D point tracker that represents videos as persistent 3D scene tracks in world coordinates, decoupling model complexity from video duration by scaling with scene geometry rather than frame count. It introduces voxelization-based de-duplication to merge co-located tracks across sliding-window boundaries, an endpoint refiner plus lightweight trajectory refiner that only decodes dense trajectories for dynamic points, and 3D WAFT, which replaces memory-heavy 4D correlation volumes with feature sampling in the scene cloud. On TAPVid-3D it beats open-source dense 3D trackers by over 20% APD on short clips and is the first 3D tracker able to track all visible points across 1000+ frame videos within 40GB GPU memory.

TAPVid-3D

research, multimodalΒ· Added 26 Sep 2026, published 24 Sep 2026

rapid7.comwriteupπŸ›‘οΈ Security

When Business Email Compromise Starts Rewriting Reality

Rapid7 previews collaborative research with Zimbra that uncovered over 50 vulnerabilities in the Zimbra Collaboration Suite, several of which let attackers impersonate senders without credentials, control inbox visibility, and alter shared documents and calendars, turning classic Business Email Compromise into active manufactured-reality attacks rather than passive mailbox monitoring. It traces the pattern through real exploited Zimbra CVEs in CISA's KEV catalog (CVE-2024-45519 postjournal command injection, CVE-2025-27915 stored XSS via calendar invite used against Brazilian military targets, CVE-2026-73570 SNMP command injection) and earlier 2022 to 2023 zero-days (CVE-2022-27925, CVE-2022-37042 path traversal plus auth bypass, CVE-2023-37580) exploited by multiple threat groups per Google's Threat Analysis Group.

Zimbra
CVE-2024-45519CVE-2025-27915CVE-2026-73570+7

AppSec, Threat IntelΒ· Added 7 Oct 2026, published 24 Sep 2026

rapid7.comadvisoryπŸ›‘οΈ Security

CVE-2026-94127: Critical Unauthenticated RCE in F5 BIG-IP APM

Rapid7's ETR writeup covers CVE-2026-94127, a critical heap-based buffer overflow (CVSS 9.8) in F5 BIG-IP Access Policy Manager that allows unauthenticated remote code execution via crafted traffic. Exploitation requires a virtual server with both an APM access policy and an OAuth profile configured, affects the data plane (including Appliance mode), and has been added to CISA KEV; F5 provides hotfixes for the 21.1.0, 17.5.0, and 17.1.0 release trains plus an iRule workaround for those unable to patch immediately.

F5 BIG-IPCVSSCISA KEV+1
CVE-2026-94127

Cloud & Infra, Identity & AccessΒ· Added 7 Oct 2026, published 23 Sep 2026

thehackernews.comadvisoryπŸ›‘οΈ Security

Cisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active Attacks

Cisco disclosed CVE-2026-76460 (CVSS 10.0), an unauthenticated API authentication bypass in Identity Services Engine (ISE) and ISE-PIC that is under active exploitation and has been added to CISA's KEV catalog with a federal patch deadline of September 19, 2026; successful exploitation can yield root command execution, and Cisco provides log-based IOC detection guidance since there is no workaround. The same disclosure batch includes 77 new CVEs, 41 in ISE and 28 in Secure Firewall (ASA/FTD/FMC), covering authenticated RCE, SQL injection, XXE, command injection, and additional REST API auth bypasses, plus a separately exploited Secure Email Gateway flaw (CVE-2026-76461, CVSS 9.8).

CVSSCISA KEV
CVE-2026-76460CVE-2026-76461CVE-2026-20176+48

AppSec, Identity & AccessΒ· Added 22 Sep 2026

simonwillison.netarticle🧠 AI

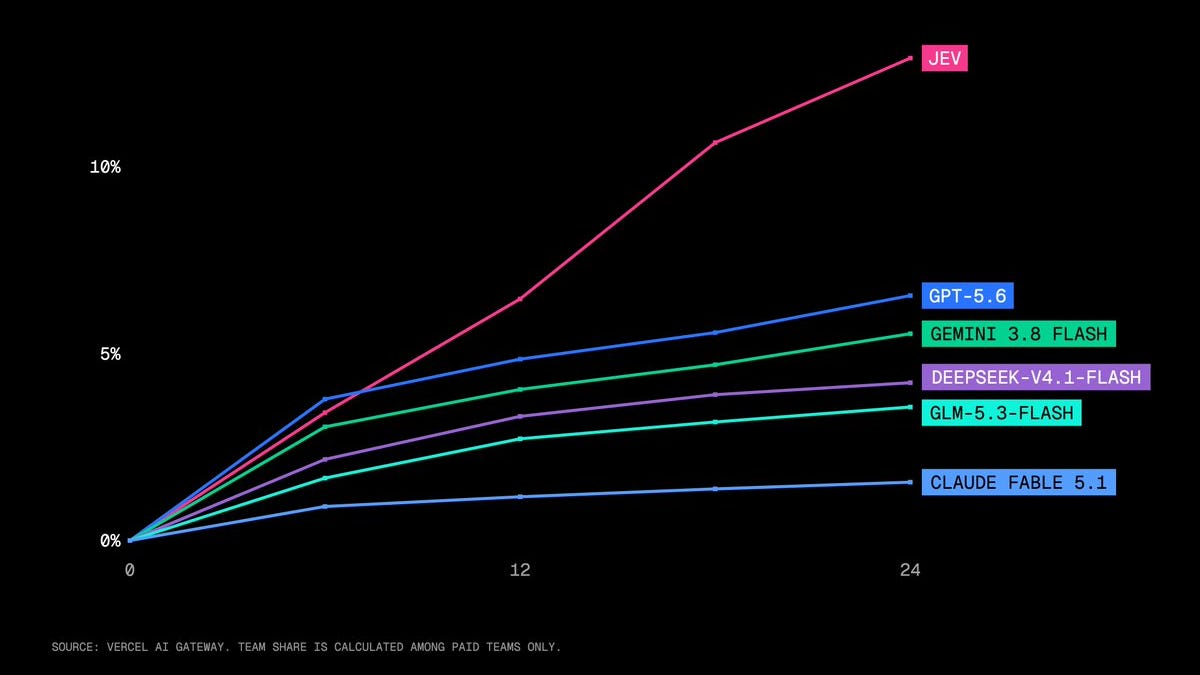
Jev introduces a new shape of LLM - System One, aka Decision Models

Simon Willison reviews Jev, a new class of model from TypeSafe AI dubbed "System One models" (or "decision models"): instead of generating text, it takes a text/structured "state" plus one or more yes/no ("Noul"), multiple-choice, or scored-range questions and returns floating point probabilities/confidence scores, priced at $0.042/million input tokens with free output. The post covers real use cases (classification, spam detection, search reranking over BM25 candidates), community experiments (jevchat, jev-leftpad, jev-2048), open-weight recreations built on Qwen 3.5 (the Kev models and JevBench benchmark), and raises concerns about the model's black-box nature and bias risk, plus Willison's own llm-typesafe plugin for the LLM CLI tool.

QwenBM25
JevTypeSafeSimon Willison+8

models, evalsΒ· Added 29 Sep 2026, published 21 Sep 2026

latent.spacearticle🧠 AI

[AINews] Here are 6 Clones of Jev in 2 days

Latent Space's AINews digest covering the rapid open-source cloning of Jev, a non-generative 'discriminative decision model' positioned as a fast System-1 complement to LLMs for routing, escalation and tool-call decisions. It catalogs six independent reproductions (Laya, DiffusionGemmaJev, Bespoke Nimble, SemIf/OpenJev, Jevlike, Kev-0.5B) built on ModernBERT, diffusion, and Qwen3.5/Qwen2.5 backbones with LoRA and contrastive/NLI-based scoring heads, plus a wider AI Twitter recap covering AGENTS.md adoption in Claude Code, coding-agent harness-design research, RSI benchmark rankings, computer-use benchmarks, and AI safety/governance news.

ModernBERTQwen3LoRA+5
JevLatent SpaceLaya+28

models, evals, agentsΒ· Added 29 Sep 2026, published 19 Sep 2026

github.comrepo🧠 AI

OmniJev/awesome-jev-gallery

An extensive, actively maintained GitHub "awesome list" cataloging the ecosystem that has grown around TypeSafe's Jev and its "System One" typed decision models β€” a non-generative alternative to chat LLMs that returns calibrated probabilities per option (Choice/Score/Noul primitives) via RLCD training and single-pass constrained decoding. It indexes dozens of open-weight reproductions (OneJev, Rizzo Flow, Laya, Jebadiah, kev), benchmarks and leaderboards (JevBench, Jev Decision Index, JevAdvBench, DecisionBench), downstream tools (browser/robot/trading agents built on the typed API), and the research lineage the design draws on (zero-shot entailment classifiers, InstructGPT's reward model, GLiNER/GLiClass, monoBERT, LLaDA, vLLM, DSPy, RouteLLM, Constitutional Classifiers). It also links commentary auditing TypeSafe's claims (accuracy vs. frontier LLM baselines, security issues found in community tools).

vLLMDSPyOutlines+13
JevTypeSafeDiogo Almeida+31

models, evals, researchΒ· Added 29 Sep 2026, published 17 Sep 2026

zerodayinitiative.comarticleπŸ›‘οΈ Security

The Apple Security Update Review for September 2026

Zero Day Initiative's monthly Apple patch review covers the September 2026 release (macOS 27/Sequoia 15.8/Tahoe 26.7, iOS/iPadOS 27 & 26.7, visionOS, watchOS, tvOS, Safari, Xcode), totaling 273 CVEs. It highlights CVE-2026-65400 (Screen Sharing Server authentication bypass, 9.8 CRITICAL, actively exploited per CISA KEV), CVE-2026-65414 (Bluetooth remote code execution, 9.8 CRITICAL, affecting all eight platforms), and CVE-2026-65346 (ImageIO arbitrary code execution via malicious image, 8.8 HIGH), plus a full CVE-by-component-by-platform table with CVSS scores where NVD/CISA-ADP has assigned them.

macOSiOSSafari+3
CVE-2026-65400CVE-2026-65414CVE-2026-65346+271

otherΒ· Added 28 Sep 2026, published 16 Sep 2026

rapid7.comadvisoryπŸ›‘οΈ Security

CVE-2026-76461: Critical Cisco Secure Email Gateway Vulnerability Exploited in the Wild

Rapid7's emerging threat response write-up on CVE-2026-76461, a critical (CVSS 9.8) SQL injection vulnerability in Cisco AsyncOS Software for Cisco Secure Email Gateway that allows an unauthenticated remote attacker to achieve root command execution by sending a specially crafted email. Cisco confirmed active zero-day exploitation and the vulnerability was added to CISA's KEV catalog the same day it was disclosed; the post provides mitigation guidance (emergency patching to 16.5.0-780) and a log-grep IOC (searching mail_logs for COPY.*TO PROGRAM) to detect exploitation attempts.

Cisco Secure Email GatewayCVSS
CVE-2026-76461CISA KEV

AppSec, Threat IntelΒ· Added 7 Oct 2026, published 15 Sep 2026

latent.spacearticle🧠 AI

[AINews] AEF-1 standard emerges for Third Party Evaluators, as Xai, OpenAI, and Anthropic all cosign

This Latent Space AINews issue (9/11–9/14/2026) centers on the AI Evaluator Forum's AEF-1 standard for independent third-party AI evaluators, published alongside Dario Amodei's personal follow-up to 'Pacing the Frontier' proposing embedded evaluators (like METR) with employee-like access at frontier labs, plus a sharp Twitter split between pacing/slowdown advocates (Bilal Chughtai, Dan Selsam) and control-first critics (Aidan Gomez, Cohere, Kevin Bass alleging conflicts of interest in the safety-eval ecosystem). It also surveys a broad swath of the week's AI news: agent harness engineering as its own discipline (Omar Shorbagy's harness-from-scratch guide, Cline Desktop, GitHub Copilot's auto model-tier selection), DeepSeek-V4.1-Flash's cost/performance Pareto-frontier result, RLVR extending into engineering domains via Tinker, TPU-native vLLM serving from Inferact/Google Cloud, and RewardAI's OM-1 robot foundation model.

vLLMLangChainCodex+2
AI Evaluator ForumAEF-1Dario Amodei+36

ai-policy, ai-safety, agentsΒ· Added 29 Sep 2026, published 15 Sep 2026

orca.securityadvisoryπŸ›‘οΈ Security

Breaking: GitLab Critical Path Traversal Flaw Exploited in the Wild β€” Patch Immediately

Details CVE-2026-85706 (CVSS 10.0), an unauthenticated arbitrary file read in GitLab CE/EE's repository commits API exploitable via a crafted file.path parameter in a single POST request, requiring only that one public project exist on the instance. It also covers CVE-2026-87719 (CVSS 9.9), an authenticated insecure deserialization bug in GitLab EE's GraphQL subscription serializer reachable via Duo Chat access that leaks stored Elasticsearch/OpenSearch credentials. Both affect GitLab versions through 19.3.1; CVE-2026-85706 is under active internet-wide scanning per WatchTowr Labs and is in CISA's KEV catalog with a federal patch deadline, with fixes in GitLab 19.1.8/19.2.6/19.3.2.

GitLabCVSSElasticsearch+1
CVE-2026-85706CVE-2026-87719CISA KEV+2

AppSec, Threat IntelΒ· Published and added 14 Sep 2026

rapid7.comadvisoryπŸ›‘οΈ Security

CVE-2026-85706: Critical GitLab Path Traversal Exploited in the Wild

GitLab patched CVE-2026-85706, a critical (CVSS 10.0) path traversal flaw (CWE-22) in the repository commits API that lets an unauthenticated attacker read arbitrary files from self-managed GitLab CE/EE instances; CISA added it to the KEV catalog on September 11, 2026 due to active exploitation, with a remediation deadline of September 14. The same patch release fixes CVE-2026-87719, a critical insecure deserialization bug (CWE-502) letting an authenticated Duo Chat user exfiltrate Advanced Search configs and credentials via a crafted GraphQL subscription argument, plus 17 other vulnerabilities. Rapid7 recommends emergency patching and post-patch compromise checks given confirmed in-the-wild exploitation.

GitLabCVSSGraphQL+1
CVE-2026-85706CVE-2026-87719CWE-22+1

AppSec, Threat IntelΒ· Added 7 Oct 2026, published 14 Sep 2026

endorlabs.comarticleπŸ›‘οΈ Security

How Should I Prioritize Software Vulnerabilities? | Blog | Endor Labs

Endor Labs blog post comparing five approaches to prioritizing software vulnerabilities: CVSS scoring, CISA's KEV catalog, Carnegie Mellon's SSVC decision tree, FIRST's EPSS exploit-prediction model, and call-graph-based reachability analysis. It cites concrete data (e.g., EPSS v3 threshold of 0.088 catches ~82% of exploited CVEs while requiring remediation of only 7.3% of known CVEs, versus patching most CVSS high/critical issues) and walks through each method's limitations, using examples like CVE-2017-0144 (EternalBlue/NotPetya) and CVE-2004-1464.

CVSSEPSSNVD+2
CVE-2017-0144CVE-2004-1464CISA KEV

AppSecΒ· Published and added 11 Sep 2026

endorlabs.comarticleπŸ›‘οΈ Security

OWASP OSS Risk 1: Known Vulnerabilities | Blog | Endor Labs

First in Endor Labs' 10-part series on the OWASP Top 10 OSS Risks, this piece breaks down "Known Vulnerabilities" (OSS-RISK-1): how CVEs get assigned and disclosed, why the 2017 Apache Struts CVE-2017-5638 unpatched flaw led to the Equifax breach of 145M+ records, and how to compare vulnerability data sources (NVD, GitHub Advisory Database, OSV). It details prioritization methods β€” CVSS, EPSS, CISA KEV, SSVC, and function-level reachability analysis β€” and shows a case study where filtering 134K findings down via reachability, fix-availability, production-code, and EPSS thresholds cut remediation work by 99.97%.

Endor LabsNVDOSV+2
CVE-2017-5638EquifaxApache Struts+2

Supply Chain, AppSecΒ· Published and added 11 Sep 2026

endorlabs.comarticleπŸ›‘οΈ Security

Combining EPSS and Reachability Analysis to Optimize Vulnerability Management | Blog | Endor Labs

Endor Labs breaks down how the Exploit Prediction Scoring System (EPSS) v3 works β€” the exploitation telemetry, exploit-DB/GitHub/Metasploit code checks, CISA KEV/Project Zero/ZDI mentions, CVSS vectors, CWE, and social-media signals it ingests to score CVE exploitation likelihood β€” and shows that an EPSS-threshold (0.088) remediation strategy fixes the same share of exploited CVEs while patching only ~7.3% of known vulnerabilities versus ~82% under a "fix all high/critical" CVSS approach. It then explains a layered workflow: use reachability analysis (call-graph based) to cut findings by ~80% to what's actually exploitable in your environment, then apply EPSS on that reduced set to rank remaining issues by real-world exploitation likelihood, including for third-party/proprietary code where reachability analysis isn't feasible.

EPSSCVSSNVD+3
CISA KEVCWE-94

AppSecΒ· Published and added 11 Sep 2026

endorlabs.comarticleπŸ›‘οΈ Security

FedRAMP Requirements for Vulnerability Management and Dependency Upgrades | Blog | Endor Labs

An Endor Labs blog post, written by a former JAB Technical Representative, details FedRAMP's Continuous Monitoring vulnerability management requirements: authenticated scanning, monthly dependency inventories, POA&M tracking, and strict remediation SLAs (High CVSS 7.0+ in 30 days, Medium in 90, Low in 180). It also covers FedRAMP's container-specific rules (hardened images, CISA KEV prohibition, pipeline/registry/runtime scanning) and outlines four practical strategies β€” reachability-based false-positive triage, EPSS-driven risk level adjustments, ROI/complexity-based upgrade prioritization, and developer-side PR gating β€” before pivoting into an Endor Labs product pitch.

Endor LabsCVSSEPSS
FedRAMPCISA KEVNIST 800-53

GRC, Supply ChainΒ· Published and added 11 Sep 2026

rapid7.comarticleπŸ›‘οΈ Security

Metasploit Wrap Up: This One Goes to Sixteen!

Rapid7's weekly Metasploit Framework update covering sixteen new modules: ten exploits (five on the CISA KEV list) targeting Cisco Secure Firewall Management Center (CVE-2026-20079 auth bypass RCE), SonicWall SMA1000 (CVE-2026-83549 chained RCE), PaperCut NG/MF (CVE-2026-81578 + CVE-2026-82078), JetBrains TeamCity agent-polling XStream deserialization RCE (CVE-2026-63077), Langflow authenticated RCE (CVE-2026-19295), MCPJam Inspector command execution (CVE-2026-23744), SimpleHelp OIDC auth bypass (CVE-2026-48558), Next.js Windows RCE (CVE-2026-75604), and SPIP SQLi/RCE flaws. It also adds a new native Kerberos relay module exploiting ESC8 (AD CS Web Enrollment) via SMB-to-HTTP coercion, a Metasploit handler-detection scanner, a Linux sandbox-evasion module, two Windows persistence techniques, and several bug fixes to the DNS and module metadata subsystems.

MetasploitCiscoSonicWall+3
CVE-2025-66516CVE-2025-54988CVE-2026-20929+12

Offensive Security, AppSecΒ· Added 7 Oct 2026, published 11 Sep 2026

wiz.ioadvisoryπŸ›‘οΈ Security

Artifactory Under Attack: In-the-Wild Exploitation of CVE-2026-42016, CVE-2026-42018 & CVE-2026-82329

Wiz Research documents active in-the-wild exploitation of three JFrog Artifactory vulnerabilities: CVE-2026-42018 (exposes an internal anonymous-user JWT via POST /access/api/v1/aws/token/), CVE-2026-42016 (token scope validation flaw allowing that JWT to be escalated to admin via POST /access/api/v1/tokens), and CVE-2026-82329 (unauthenticated admin access via POST /access/api/v1/registry/join, added to CISA KEV). Attackers chained the first two to create persistent admin accounts, deploy malicious Groovy plugins for RCE, and drop Rust-based C2 backdoors, while CVE-2026-82329 was exploited independently for configuration exfiltration, cluster join-key theft, and credential/SSH-key persistence. The post includes exact request sequences, detection signatures, affected/fixed version ranges, and remediation guidance.

JFrog ArtifactoryRust
CVE-2026-42016CVE-2026-42018CVE-2026-82329+1

AppSec, Threat Intel, Blue Team & DetectionΒ· Published and added 10 Sep 2026

aikido.devarticleπŸ›‘οΈ Security

The CVE spike across major software companies is a remediation problem

Aikido argues the widely-shared a16z/Epoch AI chart showing critical/high CVEs jumping from under 100/month to over 600/month since spring 2026 reflects AI accelerating vulnerability discovery, not a real spike in danger β€” since CISA's KEV count has stayed flat. It details how NIST's NVD, overwhelmed by volume, let its scoring backlog balloon from 13,000 to 27,000 CVEs in 18 months and pivoted to only prioritizing federal/critical/KEV-listed CVEs, while Verizon's 2026 DBIR found only 26% of confirmed actively-exploited KEV vulnerabilities were fully remediated in 2025 (down from 38%) with median patch time rising to 43 days. It illustrates the point with StyleSmuggler, an unauthenticated RCE hitting Adobe Commerce and Magento Open Source that had no CVE or vendor advisory, which Aikido Intel flagged and Aikido Libraries auto-patched more than 24 hours before Adobe's own hotfix.

Adobe CommerceMagentoAikido Security+2
StyleSmugglerCISA KEVNIST+3

AppSec, Supply ChainΒ· Published and added 10 Sep 2026

wiz.iowriteupπŸ›‘οΈ Security

Off Guard: Breaking LiteLLM from authentication bypass to cloud compromise

Wiz researchers chain three LiteLLM flaws into a full pre-auth-to-cloud-compromise path: an MCP endpoint authentication bypass (CVE-2026-59822) that grants a session with any garbage Bearer token, a custom-code-guardrail sandbox bypass leading to root RCE (CVE-2026-59821) via exec() on unsanitized admin-submitted Python, and a config-endpoint authorization gap (CVE-2026-35029). They also show pass-through endpoints can be pointed at the AWS IMDS to steal IAM credentials, bypassing IMDSv2 via header-prefix forwarding. A scan of ~3,074 internet-facing instances found 9.6% accepting the default sk-1234 master key or no auth at all, and CVE-2026-59822 is now in CISA's KEV catalog with observed in-the-wild exploitation.

LiteLLMModel Context ProtocolAWS+3
CVE-2026-59822CVE-2026-59821CVE-2026-35029+1

AI Security, AppSec, Cloud & InfraΒ· Published and added 9 Sep 2026

github.comrepoπŸ›‘οΈ Security

mukul975/cve-mcp-server

cve-mcp-server is a Model Context Protocol server that gives Claude direct access to 28 security tools spanning 24 APIs (NVD, EPSS, CISA KEV, OSV.dev, GitHub GHSA, MITRE ATT&CK, AbuseIPDB, GreyNoise, Shodan, VirusTotal, MalwareBazaar, ThreatFox, Ransomwhere, and more), fronted by a one-call triage_cve orchestrator. It computes a composite 0-100 risk score from CVSS, EPSS, KEV status, and PoC availability (with a hard CISA KEV override forcing CRITICAL/β‰₯76), supports dependency scanning via OSV, IP/domain reputation lookups with private-IP blocking, and ships an SSVC v2 gated decision mode plus audit logging and XML-bomb protections via defusedxml.

Model Context ProtocolClaude DesktopClaude Code+9
CVE-2021-44228CVE-2024-3400CVE-2023-44487+3

AI Security, Threat IntelΒ· Published and added 7 Sep 2026

github.comrepoπŸ›‘οΈ Security

cyanheads/osv-advisory-mcp-server

osv-advisory-mcp-server is an MCP server that queries the OSV.dev vulnerability database, offering single-package version checks, batch audits of up to 1000 {name, ecosystem, version} tuples for SBOM/lockfile triage, and full advisory record fetch by OSV ID (GHSA/PYSEC/RUSTSEC/GO/DSA/DLA/CVE prefixes). It surfaces CVE aliases, CVSS vectors, derived severity labels, and CWE IDs, and is designed to chain into a companion nist-nvd-mcp-server for CVSS base scores, EPSS probability, and CISA KEV status. It ships as a keyless, no-API-key tool runnable via STDIO or Streamable HTTP, with a public hosted instance and Bun/npx/Docker install paths.

Model Context ProtocolOSVBun+3
CISA KEVEPSSnist-nvd-mcp-server

Supply ChainΒ· Added 1 Sep 2026

wiz.iowriteupπŸ›‘οΈ Security

Inside 90 days of attacks on AI infrastructure

Wiz Threat Research ran honeypots across LiteLLM, Flowise, LangChain, Langflow, ChromaDB, Ollama and other AI/ML services for 90 days, capturing active exploitation of an MCP Gateway auth bypass (CVE-2026-59822) and an MCP server test-endpoint command injection (CVE-2026-42271, in CISA KEV, chainable with Starlette CVE-2026-48710 for unauthenticated RCE and linked to Qilin ransomware exploitation) used to deploy fileless cryptominers. It also documents blind prompt injection campaigns against LangChain, Flowise, OpenWebUI, and Node-RED agents that trigger OS command execution confirmed via out-of-band DNS callbacks to OAST domains.

LiteLLMLangChainFlowise+3
CVE-2026-59822CVE-2026-42271CVE-2026-48710+2

Threat Intel, Offensive Security, AI SecurityΒ· Added 3 Sep 2026, published 27 Aug 2026

orca.securityarticleπŸ›‘οΈ Security

BOD 26-04 Just Changed How Federal Agencies Prioritize Vulnerabilities.

Discusses CISA's Binding Operational Directive 26-04, which changes how U.S. federal agencies must prioritize and remediate vulnerabilities, reportedly shifting away from simple CVSS scoring toward more risk-based criteria (e.g., exploitability, KEV status). The piece explains implications for federal agency vulnerability management programs and compliance timelines.

BOD 26-04CISA

GRCΒ· Added 3 Sep 2026, published 20 Aug 2026

socket.devarticleπŸ›‘οΈ Security

Socket: White House Authorizes Private Companies to Conduct Offensive Cyber Operations

A White House presidential memorandum creates a formal DOJ/DHS-managed program letting vetted U.S. cybersecurity companies conduct 'cyber surveillance' and 'cyber effects' operations (data access, disruption, or destruction) against foreign cybercrime infrastructure under government approval, building on a March 2026 executive order. The piece covers the CFAA Β§1030(f) legal basis (per Robert Graham's analysis), the DOJ/DHS approval process via the Homeland Security Task Force's National Coordination Center, vetting and bonding requirements, and industry pushback from Kevin Beaumont and Jason Kikta over conflict-of-interest incentives when ransomware-adjacent firms are paid to both detect and disrupt threats.

CFAA Β§1030(f)BlackCatHomeland Security Task Force National Coordination Center

GRC, Threat IntelΒ· Published and added 14 Aug 2026

metr.orgarticleπŸ›‘οΈ Security

Have We Seen an Acceleration in Discoveries?

METR note that plots public discovery data in vulnerabilities, mathematics and algorithmic optimization to look for slope changes around January 2026. CVE counts rose sharply: cURL went from 9 to 36, OpenSSL from 6 to 39, Firefox from 210 to 342, Microsoft from 1,243 to 1,927 through August 2026. Exploited-vulnerability lists (CISA KEV, VulnCheck KEV) grew far less. Math shows weaker acceleration, optimization none.

cURLOpenSSLFirefox+3
METRMythosVulnCheck+5

AI Security, otherΒ· Added 29 Oct 2026, published 14 Aug 2026

github.comrepoπŸ›‘οΈ Security

ErSilh0x/VULNaware

Vulnaware is an open-source vulnerability prioritisation engine that ingests Nessus Pro, Greenbone/OpenVAS and MaxPatrol VM exports (CSV or API) plus custom CSV. It enriches findings with CISA KEV, VulnCheck KEV/NVD++, FSTEC BDU and MaxPatrol trending data, then scores them deterministically. Urgent findings go to Telegram, email digests and host-level tickets in Jira Service Management, GLPI, Znuny or osTicket. It runs as Docker containers (Flask dashboard, APScheduler worker, PostgreSQL 17).

NessusGreenboneMaxPatrol VM+3
CVE-2025-43859CISA KEVVulnCheck+3

Blue Team & DetectionΒ· Added 2 Nov 2026, published 6 Aug 2026

thehackernews.comadvisoryπŸ›‘οΈ Security

AI Security Briefing

CISA added four actively exploited vulnerabilities to its KEV catalog: a path traversal RCE in Adobe ColdFusion (CVE-2026-48282, CVSS 10.0), an unauthenticated file-upload RCE in Joomlack Page Builder CK (CVE-2026-56290, CVSS 10.0), an IDOR in Langflow allowing cross-tenant flow execution and LLM/AWS key theft (CVE-2026-55255, CVSS 6.1), and an unauthenticated arbitrary file upload in JoomShaper SP Page Builder (CVE-2026-48908, CVSS 10.0). Sysdig documented an operator chaining the Langflow IDOR with CVE-2026-33017 RCE for opportunistic, financially motivated cryptojacking/botnet activity and credential theft from an AI orchestration platform, while mySites.guru observed web shell deployment via the Joomla flaws. FCEB agencies must patch by July 10, 2026.

Adobe ColdFusionLangflowPHP+1
CVE-2026-48282CVE-2026-56290CVE-2026-55255+15

Threat Intel, AppSec, AI SecurityΒ· Published and added 18 Jul 2026

xmcyber.comarticleπŸ›‘οΈ Security

The 2026 Verizon DBIR Stopped Asking How Attackers Get in and Started Asking Where They Go

An XM Cyber analysis of the 2026 Verizon DBIR, which for the first time ran attack-graph analysis across real environments to model post-compromise privilege escalation rather than just initial access vectors. Key findings cited: exploitation of vulnerabilities overtook credential theft as the top initial-access vector (31%), 83% of privilege-escalation incidents involved no vulnerability, 16% of organizations had an 80%+ chance a low-privilege attacker could reach a key admin account, and only 26% of CISA KEV vulnerabilities were fully remediated in 2025 (down from 38%) with median remediation time up to 43 days. The piece argues security programs over-invest in patching (which addresses only ~10% of escalation techniques) versus privilege/permission hygiene (which addresses ~65%), and recommends attack-path "choke point" remediation and prioritized patching over patch-everything approaches.

XM Cyber
CISA KEVVerizon DBIR

Threat Intel, Offensive SecurityΒ· Added 3 Sep 2026, published 2 Jul 2026

orca.securityadvisoryπŸ›‘οΈ Security

Orca Security: Langflow RCE (CVE-2026-33017) Actively Exploited

Orca Security details CVE-2026-33017 (CVSS 9.8), an unauthenticated RCE in Langflow's public flow-build API (/api/v1/build_public_tmp/{flow_id}/flow) that lets attackers execute arbitrary Python via a crafted node definition, with no sandboxing. Trend Micro observed active exploitation within 20 hours of disclosure, deploying a Go-based "lambsys" binary that kills rival cryptominers, disables AppArmor/SELinux/UFW/iptables, wipes logs, harvests credentials/.env files, and installs a geo-aware XMRig miner; ~7,000 internet-exposed Langflow instances were found, the flaw is in CISA's KEV catalog, and fix guidance clarifies 1.8.2 is still vulnerable β€” users must upgrade to 1.9.0+ or the 1.9.0.dev18 nightly and rotate exposed secrets.

LangflowPythonGo
CVE-2026-33017lambsysCISA KEV+2

AppSec, Threat IntelΒ· Published and added 2 Jul 2026

github.comrepoπŸ›‘οΈ Security

XORCISM-AI/XORCISM

XORCISM is a self-hosted, open-source enterprise risk/exposure management platform (Node.js/TypeScript over SQLite/PostgreSQL/MySQL) that unifies asset inventory, vulnerability management, threat intel (STIX/TAXII), GRC (ISO 27001, NIST CSF/800-53, EBIOS Risk Manager, NIS2, DORA), incident management, and offensive/defensive testing into one continuously recomputed per-asset and enterprise risk score. It chains recon/exploitation tool connectors (nmap, nuclei, Metasploit, sqlmap) into attack-path/choke-point graphs weighted by fusion exploitability (EPSS+CVSS+KEV+public exploits), validates detection coverage via a purple-team loop against 3,750+ Sigma rules and MITRE ATT&CK/D3FEND, and quantifies ransomware impact in dollar terms via a FAIR-style model β€” with local-only Ollama AI assistants for triage, hunting, and reporting.

Node.jsTypeScriptSQLite+3
APT29SecureCodersRustinel

GRC, Offensive Security, Blue Team & DetectionΒ· Published and added 1 Jul 2026

github.comrepoπŸ›‘οΈ Security

RAPTOR

RAPTOR is an autonomous offensive/defensive security research framework built on top of Claude Code that chains static analysis (Semgrep, Coccinelle, CodeQL), binary analysis (radare2, Frida, Z3-based exploit feasibility), LLM-driven multi-stage vulnerability validation, exploit PoC generation, and patch writing into a single workflow against source code or compiled binaries. It also includes an /sca supply-chain command that enriches dependency findings with OSV, CISA KEV, EPSS, and SSVC data and emits CycloneDX SBOMs, and sandboxes LLM-generated/untrusted code execution using Linux namespaces, Landlock, and seccomp. Authored by Gadi Evron, Daniel Cuthbert, Thomas Dullien (Halvar Flake), Michael Bargury, and John Cartwright, it ships 200+ custom static analysis rules and supports multi-model LLM analysis (Claude, GPT, Gemini, Ollama).

Claude CodeSemgrepCodeQL+5
Gadi EvronDaniel CuthbertThomas Dullien+2

AppSec, Offensive Security, AI Security, Supply ChainΒ· Published and added 28 Jun 2026

snyk.ioarticleπŸ›‘οΈ Security

NVD in the AI Era: The Case for Multi-Source Vulnerability Intelligence

Snyk analyzes NIST's April 15, 2026 policy change to NVD, which replaced universal CVE enrichment with a risk-based triage model prioritizing CVEs in CISA's KEV catalog, federal-government software, and EO 14028 critical software, while deprioritizing everything else as lowest priority not scheduled. The piece details operational changes (NIST no longer routinely providing an independent CVSS score when a CNA already supplied one, and only reanalyzing modified CVEs when materially impactful) and argues this creates blind spots for scanners that depend solely on NVD, driven by CVE volume growth from about 18000 in 2020 to over 48000 in 2025 due to the federated CNA model and AI-accelerated vulnerability research.

NVDCVSSSnyk
CISA KEVExecutive Order 14028NIST

AppSec, Supply Chain, GRCΒ· Added 3 Sep 2026, published 25 Jun 2026

socket.devarticleπŸ›‘οΈ Security

Socket: pnpm 11.5 Fixes False Trust-Downgrade Alerts for npm Staged Publishes

pnpm 11.5 fixes a bug where its trustPolicy: no-downgrade check incorrectly flagged npm packages using staged publishing (a 2FA-gated release approval step) as a downgrade from trusted publishing, because pnpm inferred publishing method from the ambiguous _npmUser metadata field. The fix, prompted by a report from Kevin Deng, makes pnpm treat staged-publish approver metadata as the strongest trust signal rather than a fallback to weaker token-based publishing, reducing false-positive supply-chain alerts as npm rolls out staged publishing and trusted publishing in response to credential-theft campaigns like Mini Shai-Hulud.

pnpmnpm
Mini Shai-HuludKevin Deng

Supply ChainΒ· Published and added 13 Jun 2026

aikido.devarticleπŸ›‘οΈ Security

Full Fathom Five: The context of Anthropic’s Mythos-class public release

Aikido commentary on Anthropic's public Claude Fable 5 release. The author says it is a Mythos-class model that routes cybersecurity prompts to Opus 4.8, so benchmarking its security capability is pointless. Mythos Preview and Claude Mythos 5 stay limited to Glasswing and about 150 additional organizations. The post argues that vulnerability discovery is roughly 20% of the problem and that zero-day demand is not supply-constrained (about 30 new vulns a month, citing Resecurity). It also argues that CVE and CISA KEV-centric prioritisation is fading, and that AI tokens will mostly go to defensive scanning, exposure management and remediation rather than attacker scans.

Claude Fable 5AnthropicAikido Security+2
MythosProject GlasswingFable 5+7

AI Security, otherΒ· Added 3 Sep 2026, published 13 Jun 2026

Showing 120 of 126

Show more