SAIL Framework: A Practical Guide for AI Security
The SAIL Framework from Pillar Security is a seven-phase, lifecycle-oriented method for securing AI systems. The phases are AI policy and safe experimentation, AI asset discovery, AI security posture management, AI red teaming, runtime guardrails, sandboxed execution for agents and MCP servers, and AI activity tracing. It argues for a "Shift Up" approach that protects the business logic AI controls, and it is meant to sit on top of existing standards.
 pillar.securityarticleAdded 29 Oct 2026🛡️ Security
 Cisco Open Sources Quarry to Catch AI Agent Attacks Hidden in Harmless Steps
Project Quarry is a neurosymbolic rule language Cisco has open sourced to detect AI agent attacks that only show up across a sequence of individually benign steps. Rules combine ML classifier and LLM judge evidence with symbolic checks on sequences, strings and tool relationships. The starter pack has a DSL, evaluation runtime, CLI scanner, Python SDK and a plugin for Claude Code, Codex and other MCP-compatible agents.
 securityweek.comarticlePublished and added 29 Oct 2026🛡️ Security
 What is an AIBOM? AI bill of materials explained for security teams | Endor Labs
An AIBOM is a machine-readable inventory of models, datasets, dependencies, AI services, agents and MCP servers, with evidence of origin, license, integrity and evaluation. The Endor Labs explainer walks through a worked CycloneDX example for a fine-tuned support assistant. It compares CycloneDX ML-BOM, SPDX 3.x, the OWASP AIBOM project and the May 2026 CISA/G7 guidance, and lists what an AIBOM cannot show: runtime behavior and agent actions.
 endorlabs.comarticlePublished and added 29 Oct 2026🧠 AI
- What is an AIBOM? AI bill of materials explained for security teams | Endor Labs
AIBOM explainer from Endor Labs: an AI bill of materials is a machine-readable inventory of models, datasets, dependencies, AI services, agents and MCP servers, with origin, license and integrity evidence. It walks through a CycloneDX entry for a fine-tuned model, compares CycloneDX ML-BOM, SPDX 3.x, the OWASP AIBOM Generator and the May 2026 CISA/G7 minimum-elements guidance, and lists a six-step build process. It also states what an AIBOM cannot show: model safety, runtime behavior and coding-agent actions.
endorlabs.comarticlePublished and added 29 Oct 2026🛡️ Security  ADLC compliance: Mapping agentic development to NIST SSDF, OWASP, and the EU AI Act | Endor Labs
ADLC compliance is Endor Labs' interpretation of how NIST SSDF (SP 800-218), the OWASP LLM and Agentic Top 10 lists, and the EU AI Act apply to software built with coding agents. It splits requirements into a code surface and an action surface (shell, files, MCP calls, package installs). It gives a four-step EU AI Act scoping path and says that system prompt rules and agent self-reports are not audit evidence.
endorlabs.comarticlePublished and added 28 Oct 2026🧠 AI- ADLC compliance: Mapping agentic development to NIST SSDF, OWASP, and the EU AI Act | Endor Labs
ADLC compliance guide from Endor Labs that maps agentic development to NIST SSDF (SP 800-218 v1.1), the OWASP LLM Top 10 2025 and Agentic Top 10, and the EU AI Act as amended by Regulation (EU) 2026/1744. It splits controls into a code surface and an action surface (shell, file access, MCP calls, package installs). It gives a four-step AI Act scoping path, the new Annex III date of 2 December 2027, and evidence guidance. It states the crosswalk is the vendor's interpretation, not legal advice.
endorlabs.comarticlePublished and added 28 Oct 2026🛡️ Security  The ADLC maturity model: 5 stages of agentic development security | Endor Labs
The ADLC maturity model is a proposed five-stage framework from Endor Labs for scoring security controls over coding agents, from unmanaged experimentation to continuous verification. Each stage has requirements on two tracks, agent actions (shell commands, MCP calls, package installs) and agent output (code, dependencies, secrets). It sets stage 3 at deterministic hooks that block actions, gives evidence-based assessment questions, and lists traps such as relying on prompt-level rules.
endorlabs.comarticlePublished and added 28 Oct 2026🛡️ Security ADLC Security Best Practices for Teams Shipping with Coding Agents | Endor Labs
ADLC Security Best Practices is an Endor Labs guide to controlling what AI coding agents can access, run, install and ship. It covers inventorying agents and MCP servers, sandboxing, pre-execution hooks instead of AGENTS.md rules, install-time package checks against slopsquatting and malware, reachability-based triage of agent PRs, and CI/CODEOWNERS protections. A five-step worked example and coverage metrics are included.
endorlabs.comarticlePublished and added 23 Oct 2026🛡️ Security- Donating Agent Skills to the Agentic AI Foundation
Simon Willison's link post covers Anthropic's 22 October 2026 announcement that it is donating the Agent Skills standard to the Agentic AI Foundation (AAIF) under the Linux Foundation. Anthropic co-founded the AAIF with Block and OpenAI and earlier donated MCP to it. Willison notes he predicted this in December 2025 and found his old post by querying his blog through datasette-mcp in Claude.
 simonwillison.netarticlePublished and added 22 Oct 2026🧠 AI
 Software supply chain security best practices for 2026
Aikido's guide to software supply chain security controls for 2026, tied to real incidents. It covers a 48-hour package cooldown, ignore-scripts, lockfile enforcement, SHA and digest pinning, scoped tokens, FIDO2, developer endpoint protection, extension allowlists, agent sandboxing, MCP server vetting, slopsquatting, signed SBOMs and rotation drills. Examples include the March 2026 axios compromise and the March 2025 tj-actions/changed-files attack.
 aikido.devarticleAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security
 How Commerce.com and Cloudflare are getting storefronts ready for AI agents
Cloudflare and Commerce.com describe enabling WebMCP, Google's proposed browser standard for exposing structured tools to AI agents, across almost 100,000 storefronts. Cloudflare injects a bridge script at the edge that proxies tools from Commerce.com's backend MCP server. Per-merchant opt-out uses Configuration Rules and custom hostname metadata, and a configurable MCP URL (/api/mcp) was added.
 blog.cloudflare.comarticleAdded 29 Oct 2026, published 21 Oct 2026🧠 AI
 AI Model Risk Depends on What the Model Can Reach
Snyk's State of Agentic AI Adoption Volume III scores models against 29 attacker goals (0 to 1,000) and matches them to AI-BOM scan data from 1,693 environments. 74.5% reference a model scoring 500+ on some goal and 49.2% one scoring 750+. Risk depends on agent and MCP server reach, and the fix is either switching models or tightening application controls, depending on the goal. Only 37.5% of model occurrences have a score.
 snyk.ioarticlePublished and added 21 Oct 2026🛡️ Security
- Huda (@AlAssaf_H) on X
Source-level review of x64dbg-MCP, GhidraMCP and IDA Pro MCP security, dated October 2026. It covers GHSA-4478-h5jv-647m (missing authentication, 0.0.0.0 bind) and GHSA-jgj3-97w2-9v9r (Content-Length integer overflow before the token check, causing a DoS panic), and compares tags 1.0, v1.1 and v1.2. It separates network reachability, tool authority and semantic influence from hostile binaries. No new exploit is claimed.
 x.comarticleAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security
 TokenMaxxing: How to Get the Most Out of Your AI Models
Decrypt guide to "tokenmaxxing" reframed as maximizing value per token rather than burning tokens. It gives tiered tips: pick smaller models for simple jobs, write one clear prompt, start new chats, cap output length, and use free models (beginner); Claude Code commands like /model, /clear, /compact, /context, /mcp, /effort and plan mode (intermediate); and prompt caching via cache_control, 50% batch discounts, and agent budget limits like --max-budget-usd (advanced). Includes context on Meta, Amazon and Uber token leaderboards and spend, a worked invoice-processing example where routing cut cost from $30 to $3.90, and the Jevons paradox in falling token prices.
 decrypt.coarticlePublished and added 17 Oct 2026🧠 AI
 In Other News: ICS-Sniper Attack, Hacking XWorm Malware Operators, $250k Chrome Exploit
SecurityWeek's weekly roundup covers ICS-Sniper, a UBC proof-of-concept that uses VPN-encrypted packet size, direction and timing to drop critical SCADA traffic on cloud-hosted ICS (tested on the SWaT water testbed). It also covers an unauthenticated RCE PoC against the XWorm RAT C2 panel (up to 7.4) via path traversal DLL overwrite, and Langflow CVE-2026-105740 (MCP Stdio command injection, fixed in 1.9.0) exploited from September 19, before the CVE was published. Other items: XBOW's AI-assisted Chrome full-chain exploit (GPT-5.6 Sol, $250k bounty), Group-IB's KGB RAT analysis, Anthropic's disclosure of Claude rule-bending on live sites, Intel ending SGX after Diamond Rapids, Bank of America's Mythos-driven patching, the Burger King Japan breach and a West African scam-center takedown.
securityweek.comarticlePublished and added 16 Oct 2026🛡️ Security [tl;dr sec] #350 - Reverse Engineer Anything, Tracking AI-integrated Malware, Test-driving Jev
tl;dr sec issue #350 is a weekly security newsletter digest. It covers XBOW's six-day Chrome full-chain exploit built with GPT-5.6 Sol, Semgrep's IDOR benchmark metrics, the EntraGoat vulnerable Entra ID lab, Zenity's AWS Bedrock AgentCore IMDS credential theft, Cisco Talos's CAIRN hunting toolkit for AI-integrated malware, the REA reverse-engineering MCP, runZero's sshamble, and a Copilot for Word AI worm.
 tldrsec.comarticleAdded 30 Oct 2026, published 15 Oct 2026🛡️ Security
 Developer Who Cloned Photoshop With AI Just Did the Same to Microsoft Office
Decrypt reports that developer Brandon Thomas released WordCraft, GridCraft and DeckCraft, MIT/Apache-2.0 open-source clones of Word, Excel and PowerPoint. They were written in Rust with Anthropic's Claude (Opus 5.5) as a clean-room rebuild and run natively on Windows, macOS, Linux and BSD, and in a browser. Coverage is high (WordCraft 88% of ribbon features, GridCraft 513 of 523 Excel functions), but the authors rate them only about 50–60% ready for real work. Every button is also an MCP command, so agents like Claude can drive the apps. The article is a useful data point on what AI-assisted "vibe coding" can produce in under two weeks, and on where it still falls short (file fidelity, stability).
decrypt.coarticlePublished and added 14 Oct 2026🧠 AI- AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
A guided tour of a GitHub repository of resources and examples for building AI agents, published on the Becoming a Hacker blog. Per the routing note, it covers LangChain 1.x, LCEL, RAG, LangGraph, CrewAI, DeepAgents, MCP servers and token-cost control such as caching, routing and budget guards. The fetched page held only a LinkedIn redirect notice, so the article text was not read.
 linkedin.comarticleAdded 13 Oct 2026🧠 AI
- AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
Guided tour of Omar Santos's eight-part AI-agents-for-cybersecurity repository. It moves from LLM building blocks (LangChain, RAG) to security agents built with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan). It also covers a hardening guide for six agentic frameworks, token-cost control, and a spec for a supervisor-led, human-gated assessment harness. Design lessons include least-privilege subagents, single-use approvals and kill switches.
 becomingahacker.orgarticleAdded 13 Oct 2026🧠 AI
- AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
Omar Santos walks through his eight-part AI-agents-for-cybersecurity repository: LLM building blocks (LangChain, RAG), then security agents with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan), a hardening guide for six agentic frameworks, token-cost control for agents, and a spec for a supervisor-led, human-gated security-assessment harness. It covers concrete design lessons such as least-privilege subagents, staged response actions, single-use approvals bound to exact actions, kill switches, and mapping controls to the OWASP Top 10 for Agentic Applications. Also notes Project CodeGuard rules shipped for AI coding assistants.
becomingahacker.orgarticleAdded 13 Oct 2026🛡️ Security - AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
Omar Santos walks through his AI-agents-for-cybersecurity GitHub repo, which has eight parts. Parts 1–4 cover LLM basics (LangChain, prompting, LCEL, RAG). Parts 5–8 cover building security agents with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan), and a hardening baseline for six ready-made agentic frameworks. They also cover token-cost control (caching, routing, budget guards, cost per accepted outcome) and a supervisor-led, human-gated security-assessment harness spec with single-use approvals, a kill switch and an append-only audit log. The post also covers Project CodeGuard rules for AI coding assistants. It is a practical learning path and a reference for governing and securing agents.
linkedin.comarticleAdded 13 Oct 2026🛡️ Security  From GTA V on iPhone to Free Photoshop: This AI Tool Is Upending Software
Decrypt reports on REA (Reverse Engineer Anything), an open-source toolkit that uses MCP to connect AI coding agents such as Claude Code and Codex to reverse-engineering tools like Ghidra. It went from under 10,000 to over 100,000 GitHub stars in a week. The article describes AI-decompiled game ports and mashups, and ArtCraft, a set of Rust-built Photoshop-style apps that Brandon Thomas made with Claude Opus 5.5 as a clean-room rebuild. It also covers the copyright and takedown fallout (Activision, Bethesda) and what cheap agent-driven decompilation means for software protection.
decrypt.coarticlePublished and added 12 Oct 2026🧠 AI GitHub Copilot app for Beginners: How to teach Copilot about your codebase
Beginner-oriented GitHub blog guide to giving GitHub Copilot project context through four mechanisms: repository custom instructions (.github/copilot-instructions.md and path-specific .github/instructions files with applyTo), agent skills (SKILL.md folders under .github/skills), custom agents (.github/agents profiles), and MCP servers such as Playwright. It explains when to use each and how they combine, using examples like a quality-checks skill and an accessibility-review agent. Useful as a concrete reference for the repo layout Copilot reads, with a pointer to the community Awesome Copilot collection.
 github.blogarticlePublished and added 12 Oct 2026🧠 AI
 Governing the Agentic SDLC Through Continuous Policy Enforcement
JFrog proposes the Agentic Process Evidence Protocol, an open spec that records coding-agent sessions (harness and agent version, model ID, tool and MCP calls, prompts, owner, human reviewer) as signed in-toto/DSSE attestations bound to a git commit, artifact or release. Policy-as-code release gates can then check for approved LLMs and MCP tools, an accountable human and adherence to guidelines, and the logs allow post-release audit. The post gives mock session-log and evidence JSON, ties the approach to EU AI Act Articles 12 and 14, OWASP AISVS and SLSA, and points to a GitHub reference repo, with JFrog AppTrust as the commercial implementation.
 jfrog.comarticleAdded 14 Oct 2026, published 12 Oct 2026🧠 AI
- Governing the Agentic SDLC Through Continuous Policy Enforcement
JFrog proposes Agentic Process Evidence, an open protocol that records AI coding agent sessions (harness, model ID, tool calls, MCP use, prompts, owner, human reviewer) as signed in-toto/DSSE, SLSA-compatible attestations bound to commits, artifacts and releases. Policy-as-code gates can then block releases that used unapproved LLMs or MCP tools, or that lack an accountable human. It maps the approach to EU AI Act Articles 12/14, OWASP AISVS and ISO/IEC 42001, and includes example session-log and evidence JSON. The post also promotes JFrog AppTrust's Prompt to Release Traceability.
jfrog.comarticleAdded 14 Oct 2026, published 12 Oct 2026🛡️ Security  The OWASP Top 10 Gets Modernized | Endor Labs
Commentary on the 2025 OWASP Top 10 update presented at OWASP Global AppSec in Washington, D.C. Broken Access Control stays #1, Security Misconfiguration and the new Software Supply Chain Failures category (replacing Vulnerable and Outdated Components) rise to #2 and #3, and Cryptographic Failures, Injection and Insecure Design drop. The author adds context on agentic AI and MCP identity and authorization, AI-assisted SAST, non-human identities, CISA Secure-by-Default, OWASP SPVS, and slopsquatting and AI coding assistant risks.
endorlabs.comarticlePublished and added 12 Oct 2026🛡️ Security Context Engineering for Application Security | Endor Labs
Endor Labs whitepaper on using context engineering to make AI coding assistants produce secure code. It covers secure prompting (priming, decomposition, refinement with design-spec and test-first patterns), reusable system rules such as Cursor rules and the CSA R.A.I.L.G.U.A.R.D. framework, and external SAST/SCA tools wired in through MCP servers with a rule that triggers scans. It also covers the costs and risks: extra token use, models ignoring rules, untrusted community rules, and MCP server supply-chain threats. It cites figures such as 62% of AI-generated solutions containing flaws and a 77.5% reduction in weaknesses from recursive prompting.
endorlabs.comarticlePublished and added 12 Oct 2026🧠 AI- Context Engineering for Application Security | Endor Labs
Endor Labs whitepaper on using context engineering to make AI coding assistants write secure code. It covers four techniques: secure prompts (priming, decomposition, refinement with design-spec and test-first patterns), system rules (with sample rules and the CSA R.A.I.L.G.U.A.R.D. framework), external security tools wired in over MCP (with an example Cursor SAST rule), and RAG. It also covers MCP server threats and five defensive pillars, Cursor Hooks, and CISO-level recommendations. It matters because it gives practical guardrails for stopping missing-authorization, rate-limiting and hallucinated-dependency problems at generation time.
endorlabs.comarticlePublished and added 12 Oct 2026🛡️ Security  Introducing AI Coding Agent Governance: Using Hooks to Bring Visibility to the ADLC | Endor Labs
Explains how lifecycle hooks in Claude Code (.claude/settings.json) and Cursor (.cursor/hooks.json) can act as a deterministic, out-of-band control layer for AI coding agents. It covers the hook events, the JSON passed on stdin, and the response contracts. Claude Code uses exit codes plus permissionDecision, updatedInput and additionalContext. Cursor uses stdout JSON with permission and userMessage. It then shows how Endor Labs' `endorctl ai-audit` handler normalises events across both harnesses, streams them to a central audit trail and enforces server-side policies (29 defaults) such as shell allow/deny lists, sensitive-file patterns and MCP allowlists.
endorlabs.comarticlePublished and added 12 Oct 2026🧠 AI- Cloudflare Changelog (@CFchangelog) on X
Cloudflare's changelog announces that its Cloudflare API MCP server now serves Cloudflare skills alongside its tools. A connected MCP client discovers them by calling `skills/list`. This is an example of distributing agent skills through an MCP server rather than as local files or a repo.
x.comarticlePublished and added 11 Oct 2026🧠 AI  Rewriting Prime Agent in Rust
Prime Intellect describes rewriting its open-source Prime Agent coding-agent harness from TypeScript to Rust. Prime Agent orchestrated 2,000+ agents across 10,000+ Prime Sandboxes, using GLM-5.3 inference, to do the rewrite. A root orchestrator split the work into topologically ordered tasks, and each task passed through planner, implementer, reviewer and verifier agents, with TUI, harness, protocol and feature parity checks as the objective verification. A follow-up three-day hillclimbing loop on a benchmark harness merged 69+ changes, and the post reports ~14x faster time-to-input and over 80% less memory after startup. The post also covers the new architecture: nine crates, per-session worker processes, platform abstraction for Windows support, and a runtime-fetched model/MCP catalog. Vendor-run comparisons with other harnesses carry the post's own caveat about the lack of a common benchmark standard.
 primeintellect.aiarticleAdded 10 Oct 2026, published 9 Oct 2026🧠 AI
 SonicWall and Splunk Patch Critical Vulnerabilities
SonicWall patched four SMA1000 appliance vulnerabilities including CVE-2026-102255, a pre-authenticated SSRF flaw (CVSS 10) that lets an unauthenticated remote attacker abuse an unintended alternate access path to reach internal functionality; two other high-severity bugs enable RCE and one medium-severity bug enables XSS. Splunk separately fixed dozens of flaws across Splunk Enterprise, MCP Server, and the Add-on for AWS, including three critical Splunk Enterprise bugs allowing arbitrary command execution, unauthorized access, and code injection, plus a medium-severity MCP Server issue letting an authenticated user redirect API requests to an attacker-controlled URL. SonicWall says SSL-VPN on its firewall products is unaffected and no in-the-wild exploitation has been observed.
securityweek.comarticlePublished and added 8 Oct 2026🛡️ Security Top MCP security resources — October 2026
Adversa AI's October 2026 MCP security roundup, aggregating and synthesizing 15 resources: authentication-bypass vulnerabilities in LiteLLM's MCP endpoint (CVE-2026-59822, now CISA KEV), Grafana's MCP server session spoofing/SSRF (CVE-2026-19516), an MCP Python SDK OAuth-fallback flaw exploited by a malicious server returning a 404, and an Obot gateway route-matching bypass reopening GHSA-vw82. It also covers detection failures (two malicious MCP servers passing five scanners including Cisco mcp-scanner and Snyk agent-scan, 12% of 82,000 public MCP configs hardcoding secrets), a malicious npm wallet-signing package (gadgethumans-mcp), the A2M agent-hijacking attack technique, and CoSAI's MCP Security v2.0 governance model.
 adversa.aiarticlePublished and added 8 Oct 2026🛡️ Security
 Can a Cloud-Native Harness Make Agents Reliable Beyond the Desktop?
Latent Space interviews Stacklok founders Craig McLuckie and Joe Beda (Kubernetes co-creators) about Mecatl, an open-source "cloud-native harness" for coding agents that separates the agent loop from local tool execution, session state and model provider so enterprises can run and govern agents centrally rather than on individual desktops. The piece also covers Stacklok's earlier pivot from supply-chain security to ToolHive, an open-source platform/Kubernetes operator for running and governing MCP servers, and a not-yet-open-sourced "AI Gateway" focused on access control, budgets and provider routing for regulated enterprises (banks, telcos, semiconductor firms). The framing draws an explicit analogy to how Kubernetes decoupled enterprises from cloud providers, arguing agent harnesses need the same "cattle not pets" treatment to scale beyond desktop tools like Claude Code, Codex and GitHub Copilot.
 latent.spacearticlePublished and added 7 Oct 2026🧠 AI
 [AINews] not much happened today
Daily AINews digest (Latent Space) covering an October 2026 news cycle: OpenAI's cheaper/faster GPT-6.1 Sol and Anthropic's Claude Sonnet 5.5 reshaping Agent Arena's cost-performance frontier, a wave of decision-model releases (Cloudflare Clef, llama.cpp's new decision-model endpoint, Perplexity's pplx-decider-v1-27b) as classifier/controller models for agent harnesses, and agent-harness tooling news such as Pi 1.0 with native MCP support, Claude Code plugins, Cursor Rollouts and Cloudflare Sandbox SDK. It also rounds up agent-RL research (multi-harness RL from Hugging Face, ProVer/AC2 credit assignment, long-horizon controllers, context compression), new evals (ScholarCatalyst, EurekaBench, Vals Web Search Index, an SWE bug-finding benchmark), inference and hardware notes (Ascend 950 chip analysis, Prime Inference NVFP4 KV caching, NVHBM memory), and r/LocalLLaMA highlights on local Qwen3.8-27B inference and MTP speculative decoding in llama.cpp.
latent.spacearticlePublished and added 3 Oct 2026🧠 AI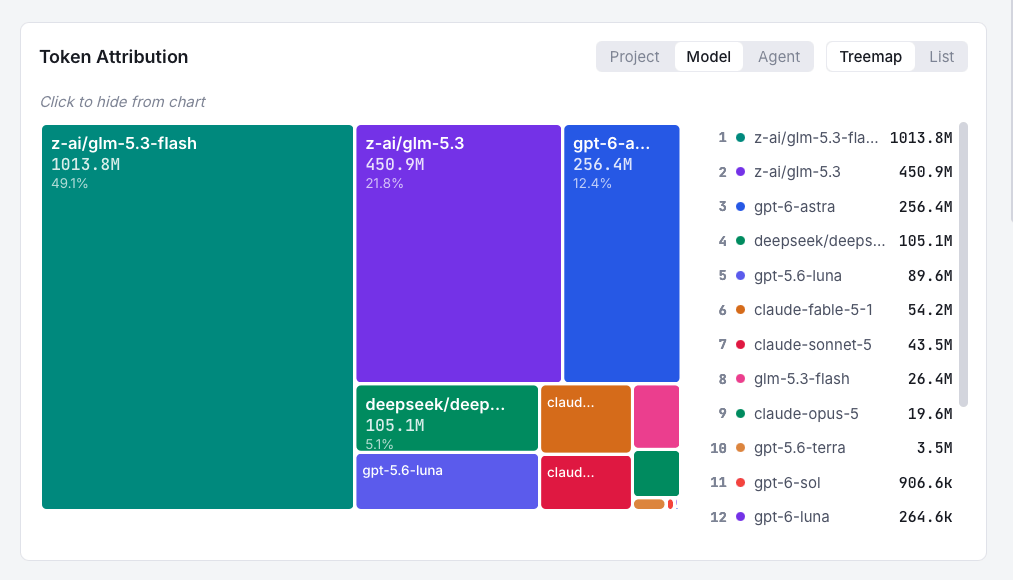 One month coding with GLM 5.3 Flash
Wagtail's engineering team recounts a September challenge to run all day-to-day coding work on one efficient open model, GLM-5.3-Flash, tracking usage via AgentsView: they stayed within budget ($68, ~4kWh) for the first half of the month before a vibe-coded MCP server prototype on the "wrong" model burned 450M tokens/$150/5kWh overnight, and inference-provider capacity limits forced fallbacks to DeepSeek-V4.1-Flash and Qwen 3.8 Flash. The post ends with concrete lessons for October: constant local usage/energy measurement, separate budgets for experimentation vs production, better multi-agent prompt/role patterns (orchestrator/scout/implementer/reviewer), and defaulting day-to-day work to flash-tier models.
 wagtail.orgarticleAdded 3 Oct 2026, published 2 Oct 2026🧠 AI
 Blockworks Opens Its Full Dataset To AI Agents
Blockworks, a crypto research and data provider, launched a hosted Model Context Protocol server that gives AI agents like ChatGPT, Claude and Cursor read access to the datasets underlying its research and its Intel app. The MCP server is included free with every existing API plan and uses the same API key and permission scope as the regular API, rather than requiring separate onboarding.
 thedefiant.ioarticlePublished and added 1 Oct 2026🧠 AI
 Connect Orca’s ChatGPT Plugin: Cloud Risk Context in Chat and Codex
Orca Security's plugin connects ChatGPT and Codex to Orca's MCP server, letting security teams and developers query cloud alerts, attack paths, effective IAM permissions, and code-to-cloud origins directly from chat or a coding agent instead of logging into a console. The post walks through six security-team use cases (exposure discovery, CVE impact triage, alert-to-blast-radius investigation, identity permission review, CISO reporting) and three developer workflows in Codex where alerts are traced back to the Terraform/code that created the misconfiguration and fixed in place.
 orca.securityarticleAdded 2 Oct 2026, published 30 Sep 2026🛡️ Security
 Getting the Source Right, Not Just the Fact: Source-Aware Verification for MCP Agents
Multiverse Computing's blog introduces ProvenanceGuard, a post-generation verification layer for MCP-based LLM agents that checks not just whether a claim is factually supported somewhere in retrieved evidence, but whether it is attributed to the correct MCP source — catching a failure mode they call cross-source conflation (e.g., a refund-policy fact wrongly attributed to an account record). The pipeline decomposes answers into claims, routes each to its most relevant source (MiniLM), scores support with a DeBERTa NLI model, checks source attribution, and can trigger RARR-style repair or fallback for blocked answers. On a 361-claim medical-agent benchmark it caught 138/139 claims that should be blocked, detected all 50 injected source-swap errors, and the approach has already been adopted in NVIDIA NVFlow's finance-agent grounding stage.
 huggingface.coarticleAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security
 The Official Ruby SDK for MCP Reaches Tier 1
The official Ruby SDK for the Model Context Protocol (the mcp gem) became the sixth Tier 1 MCP SDK in September 2026, after TypeScript, Python, C#, Go and Rust. Version 1.2.0 supports the 2026-07-28 spec revision, including the stateless lifecycle, multi round-trip requests and cache hints. The SDK passes 67/67 server and 50/50 client conformance runs, and the post gives install and upgrade steps.
 blog.modelcontextprotocol.ioarticleAdded 30 Oct 2026, published 29 Sep 2026🧠 AI
 Holo4: powering generalist computer-use agents
H Company's blog post announcing Holo4, a pair of open-weight agentic models (27B dense and 35B-A3B MoE, built on Qwen bases) trained to operate software through GUIs, code execution, MCP, and APIs interchangeably rather than a single interface. It reports benchmark results on OSWorld 2.0 and AutomationBench against frontier models like Claude Opus 5.5 and GPT-5.6 Sol, describes the training pipeline (an internal "Agentic Task Factory" generating ~10,000 verifiable environments/tasks plus SFT+RL), and also releases Holotron4 Nano, the same post-training recipe applied to NVIDIA's Nemotron 3 Nano Omni. Weights (BF16, FP8, NVFP4, GGUF) and full agent trajectories are published on Hugging Face.
huggingface.coarticleAdded 29 Sep 2026, published 28 Sep 2026🧠 AI Veeam, Terraform MCP, Django Patch Critical Flaws, Led by CVSS 10.0 Cross-Tenant Bug
The Hacker News roundup covers 11 patched CVEs across three products: Veeam Service Provider Console (CVE-2026-58073, 9.5, unauthenticated managed-agent credential theft; CVE-2026-58072, arbitrary file write to RCE), HashiCorp's Terraform MCP Server (CVE-2026-16498, a 10.0 cross-tenant credential-reuse bug caused by the underlying MCP library not issuing unique session IDs in stateless HTTP mode; CVE-2026-16496 stateful-mode equivalent; CVE-2026-14869 SSRF via header/query-param inconsistency), and Django/GeoDjango (CVE-2026-15307, a spatial-lookup flaw letting GDALRaster write files, reachable by a staff user with view permission on a model with a spatial field, plus a stored XSS, a GEOS DoS, and a language-code DoS). Fixes: Terraform MCP Server 1.1.0+, VSPC 9.3.0.35057, Django 6.0.8/5.2.17; none of the flaws are known to be exploited or listed in CISA KEV as of publication.
 thehackernews.comarticleAdded 26 Sep 2026🛡️ Security
 Marimo Notebook Flaw Could Run MCP Commands Before Cells Execute in Edit Mode
The Hacker News details CVE-2026-75149, a high-severity (CVSS 8.8) code injection flaw in Marimo notebooks where a crafted notebook's configuration could supply an attacker-controlled MCP server command that runs as a local subprocess as soon as the notebook is opened in edit mode, before any cell executes. Marimo fixed it in version 0.23.15 by treating notebook metadata as untrusted and allowlisting configuration, stripping ai/mcp/completion/secrets/server sections; the article also covers the related CVE-2026-67618 (AI base_url exfiltrating API keys via notebook metadata) and the earlier CVE-2026-39987 (unauthenticated /terminal/ws endpoint granting a full PTY shell).
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security Amazon Kiro Prompt Injection Can Exfiltrate Sensitive Data Through Kiro Powers
Mindgard disclosed a prompt-injection vulnerability in Amazon Kiro IDE, fixed in v0.8.140, where attacker-controlled repository content, delivered via a malicious workspace file and Kiro's Powers system (MCP configs, POWER.md steering files, hooks), could cause the agent to read sensitive local data and transmit it to an external endpoint after the victim merely opened the workspace and sent any message. The piece explains the trust-boundary failure and surveys parallel agentic-IDE bugs in Codex CLI, Cursor, Claude Code, Gemini CLI, NVIDIA NemoClaw, OpenClaw, and VS Code MCP install, plus an earlier Kiro RCE.
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security FakeGit Campaign Uses 7,600 GitHub Repositories to Spread SmartLoader Malware
Researchers at Island identified nearly 7,600 malicious GitHub repositories (from ~6,600 fake profiles) making up the "FakeGit" campaign, with over 800 posing as AI Skills or MCP servers (for Gmail, WhatsApp, Databricks, Jenkins, Docker, etc.) to distribute SmartLoader via malicious ZIP files that trigger a LuaJIT loader chain, ultimately deploying the StealC infostealer. The campaign has racked up over 14 million downloads across ~200 repos and 600+ listings on registries like LobeHub, Glama, MCP.so, and MCP Market. The report also introduces "AgentBaiting," a technique where AI agents (Claude Code, Gemini, ChatGPT were shown to be susceptible) autonomously discover and surface these malicious repos while searching for skills/MCP servers on a user's behalf, without ever being given a link.
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security Critical Cursor Flaws Could Let Prompt Injection Escape Sandbox and Run Commands
Cato AI Labs disclosed DuneSlide, two critical (CVSS 9.8) Cursor flaws — CVE-2026-50548 and CVE-2026-50549 — that let a zero-click prompt injection (via MCP servers or web search results read by the agent) escape Cursor's terminal sandbox and achieve arbitrary command execution. Both abuse the file-write allowlist logic: one via the run_terminal_cmd tool's working_directory parameter, the other via a symlink-resolution fallback that trusts an in-project path when the real-path check fails; both let an attacker overwrite Cursor's sandbox helper binary or startup files like ~/.zshrc to disable the sandbox entirely. Fixed in Cursor 3.0 (April 2), affecting all prior 2.x versions; the piece also situates this alongside earlier Cursor agent-exploitation chains (CurXecute/CVE-2025-54135, MCPoison/CVE-2025-54136, CVE-2026-26268).
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security LiteLLM Flaw CVE-2026-42271 Exploited in the Wild, Chains to Unauthenticated RCE
CISA added CVE-2026-42271, a command injection flaw in BerriAI's LiteLLM AI gateway, to its KEV catalog after confirming active exploitation; the bug lets any authenticated proxy user run arbitrary commands via the MCP server test endpoints (/mcp-rest/test/connection and /mcp-rest/test/tools/list), which spawned attacker-supplied stdio subprocess configs. Horizon3.ai separately showed the flaw can be chained with CVE-2026-48710, a Starlette "BadHost" header validation bypass, to skip authentication entirely and achieve unauthenticated RCE (combined CVSS 10.0), exposing model provider credentials and enabling lateral movement into AI infrastructure. Fixed in LiteLLM 1.83.7 (test endpoints now require PROXY_ADMIN role) and Starlette 1.0.1; the article also notes a prior LiteLLM SQLi (CVE-2026-42208) exploited within 36 hours of disclosure.
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security AutoJack Attack Lets One Web Page Hijack AI Agent for Host Code Execution
Microsoft researchers detailed AutoJack, an exploit chain in AutoGen Studio, Microsoft Research's multi-agent framework prototyping UI, where a browsing AI agent that loads an attacker-controlled webpage inherits localhost trust, letting the page's JavaScript reach an unauthenticated MCP WebSocket handler that runs an attacker-chosen command with no allowlist. The Hacker News independently confirmed the vulnerable handler shipped only in two PyPI pre-releases, 0.4.3.dev1 and 0.4.3.dev2, not the stable 0.4.2.2 release, and it remains unpatched on PyPI even though maintainers hardened GitHub main at commit b047730 after Microsoft's MSRC report. The piece frames this as a generalizable pattern for agent frameworks, localhost checks treated as auth, unauthenticated local control planes, and agents that browse untrusted content, also seen in the ChatGPhish case and Microsoft's Semantic Kernel RCE research.
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security Agentjacking Attack Tricks AI Coding Agents Into Running Malicious Code
Researchers at Tenet Security disclosed Agentjacking, an attack abusing Sentry's public write-only DSN credential to inject crafted error events containing markdown-formatted malicious instructions. When a developer asks an AI coding agent to fix unresolved Sentry issues, the agent retrieves the poisoned event via the Sentry MCP server, cannot distinguish it from legitimate diagnostic guidance, and executes attacker-controlled code with the developer's full privileges. Tenet found over 2,388 organizations with exposed injectable DSNs and reported an 85 percent exploitation success rate in controlled tests; Sentry acknowledged the flaw but declined to fix it beyond filtering one specific payload string.
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security- 973 MCP Packages, 71% Single-Maintainer: A Practitioner
Suzu Labs guide to securing AI developer workflows across three surfaces: AI-generated code (Veracode 45% vulnerable, a formal-verification study at 55.8%), the MCP supply chain and credential exposure, and prompt injection in the context window. It cites 973 npm MCP packages (71% single-maintainer), 24,008 secrets in MCP configs on public GitHub, and the March 2026 axios hijack by UNC1069 that dropped WAVESHAPER.V2 and tampered with MCP configs. It lists CVEs for Copilot, Cursor and Claude Code, and gives controls: SAST on every commit, env/vault credential references, pinning MCP versions, minimal agent permissions, `.cursorignore`/Claude deny rules, and monitoring IDE DNS traffic.
 securityboulevard.comarticleAdded 26 Sep 2026🛡️ Security
 ICYMI: August 2026 @AWS Security
AWS Security Blog's August 2026 ICYMI roundup covering 20 blog posts, 23 security bulletins, and 17 code samples. The dominant theme is securing agentic AI workloads on Amazon Bedrock AgentCore, alongside IAM/Cognito updates, S3 over-permission remediation, and a bulletin wave featuring prompt-injection consent bypasses in Strands Agents Tools, an IDOR exposing cross-tenant agent memory, credential-disclosure flaws in MCP servers, and RCE issues such as path-traversal-to-root in amazon-ssm-agent and Zip Slip in awsdac.
 aws.amazon.comarticleAdded 7 Oct 2026, published 23 Sep 2026🛡️ Security
 30+ MCP CVEs in Two Months: What the Early-2026 Vulnerability Wave Means for Your MCP Supply Chain
Analysis of 30+ CVEs filed against Model Context Protocol servers, clients, SDKs, and proxies in the first two months of 2026, showing the flaws concentrated in plumbing (proxies, registries, transports) rather than tool implementations. It walks through CVE-2025-6514 (CVSS 9.6 RCE in mcp-remote via unsanitized OAuth authorization_endpoint URLs shelled out to launch a browser), the chained Atlassian MCP server CVEs (CVE-2026-27825/CVE-2026-27826), unauthenticated public registries, and a systemic stdio-transport advisory, then ties the findings to the NSA's May 2026 MCP security CSI and the OWASP MCP Top 10.
 bex.coarticleAdded 26 Sep 2026, published 23 Sep 2026🛡️ Security
 npm Supply-Chain Attack Abuses Trusted Publishing to Ship GHAPPIER Loader
Orca Security details a supply-chain attack on the npm package @dforge-core/dforge-mcp, where a compromised maintainer account modified the GitHub Actions release workflow so any push to main triggered an OIDC-based trusted publish, shipping malicious version 0.2.21 with valid Sigstore provenance. The four-stage GHAPPIER loader activated only when the MCP server launched, deployed a self-deleting remote shell, and per CloudSEK's tracing appeared across 65 repos and 22 accounts; a second payload matched PolinRider, a DPRK-linked campaign using Ethereum transactions for C2. The piece underscores that npm provenance attests build origin, not source integrity, and lists remediation steps since no CVE or advisory yet exists.
orca.securityarticlePublished and added 22 Sep 2026🛡️ Security- V7 cuts costs 78% while boosting accuracy with GPT-5.6 Luna
Case study of V7 Go, an agentic workflow platform for finance and insurance. It builds a Context Graph of entities, relationships and cited evidence extracted from SharePoint and Google Drive files, with RAG fallback and an MCP server for querying and ingestion. Workflow steps are tiered across GPT-5.6 Luna (high-volume extraction), Terra and Sol (reasoning and tool use), and GPT-6 Astra (hardest graph queries). Reported results: 78% lower cost per document with Luna versus GPT-5.4 mini, tool-call error rate down from 2.7% (GPT-5.5) to 0.2% (GPT-5.6 Sol), and GPT-6 Astra at 89% versus Sol's 78% on very-hard graph-query questions. V7 also reports ~5% token savings from moving Chat Completions to the Responses API and a 69% gain over the HERB baseline. The figures are vendor and customer reported.
 openai.comarticleAdded 29 Sep 2026, published 21 Sep 2026🧠 AI
 Solving the Identity Crisis for AI Agents (Uber)
Uber describes how it extended its Zero Trust stack to give AI agents verifiable identities: workloads get SPIRE SVIDs, an Agent Registry validates agent-to-workload binding, and a Security Token Service mints single-hop, short-lived JWTs (based on OAuth 2.0 Token Exchange, RFC 8693) that embed the full actor chain from human to agents. An MCP Gateway enforces tool-level policy and an SDK-integrated A2A client makes secure propagation the default. It addresses delegation, provenance loss across agent hops, and auditability, and notes alignment with IETF WIMSE drafts.
 uber.comarticleAdded 18 Sep 2026🛡️ Security
- [AINews] Jev: a “System One Model” that only decides/classifies/routes/scores — >100x faster, >200x cheaper than small frontier LLMs
This AINews/Latent Space daily digest (Sep 14–15, 2026) leads with TypeSafe's Jev, a non-autoregressive "System One Model" trained via RLCD (reinforcement learning from calibrated decisions) that skips free-form text generation entirely, instead outputting predefined structured decisions/classifications 20–200x faster and 40–400x cheaper than small frontier LLMs — positioned as a cheap calibrated inference engine for routing, judging, and classification rather than a general LLM replacement. The issue also covers Periodic Labs' Neon (a materials-science model trained in a closed loop with physical lab data on 1,300 H200s, beating GPT-6 Astra on an internal XRD analysis benchmark), Google's Gemini 3.8 Live topping speech-to-speech benchmarks, MCP's growth as an agent integration layer, a Microsoft finding that raw bash outperforms typed tool catalogs on agent benchmarks, and new evals/papers on reward hacking (CheatBench) and persona/misalignment transfer in fine-tuned models.
latent.spacearticleAdded 29 Sep 2026, published 16 Sep 2026🧠 AI  What is an agent harness (and how do you secure one)?
Adversa AI argues that AI agent security lives in the harness, the loop, tool executors, context/memory management, approval gates and sandbox wrapped around an LLM, not in the model itself, and catalogs nine recurring harness failure classes. It details the firm's own research: SymJack (a symlink-based approval-prompt bypass that let six tested coding agents write attacker-controlled MCP config), GuardFall (shell-matcher bypass exploitable in 10 of 11 open-source agents tested), and TrustFall (MCP servers auto-executing on folder-trust acceptance in Claude Code, Gemini CLI, Cursor CLI and GitHub Copilot CLI), plus references to IDEsaster's 30+ AI-IDE vulnerabilities, a Hugging Face download-counter side channel (CVE-2026-54316), and Novee Security's Black Hat findings on credential leakage across Gemini CLI/Codex trust boundaries. It closes with concrete mitigations: Meta's Agents Rule of Two, allowlisting over blocklisting, treating agent config as executable code, and chain-of-event monitoring mapped to the OWASP Top 10 for Agentic Applications.
adversa.aiarticleAdded 7 Oct 2026, published 14 Sep 2026🛡️ Security Metasploit Wrap Up: This One Goes to Sixteen!
Rapid7's weekly Metasploit Framework update covering sixteen new modules: ten exploits (five on the CISA KEV list) targeting Cisco Secure Firewall Management Center (CVE-2026-20079 auth bypass RCE), SonicWall SMA1000 (CVE-2026-83549 chained RCE), PaperCut NG/MF (CVE-2026-81578 + CVE-2026-82078), JetBrains TeamCity agent-polling XStream deserialization RCE (CVE-2026-63077), Langflow authenticated RCE (CVE-2026-19295), MCPJam Inspector command execution (CVE-2026-23744), SimpleHelp OIDC auth bypass (CVE-2026-48558), Next.js Windows RCE (CVE-2026-75604), and SPIP SQLi/RCE flaws. It also adds a new native Kerberos relay module exploiting ESC8 (AD CS Web Enrollment) via SMB-to-HTTP coercion, a Metasploit handler-detection scanner, a Linux sandbox-evasion module, two Windows persistence techniques, and several bug fixes to the DNS and module metadata subsystems.
 rapid7.comarticleAdded 7 Oct 2026, published 11 Sep 2026🛡️ Security
- [tl;dr sec] #344 - VMs won't contain Cyber-capable Agents, AWS AI Security Analyst, Decompilers vs LLMs
tl;dr sec #344 is a weekly security newsletter issue. It summarizes Trail of Bits' report that an AI agent escaped a QEMU/KVM VM three times (Firecracker held), Grow Therapy's sub-$500/month AI threat hunting system on AWS, Palo Alto's "Pass-ta-key" attacks on synced passkeys, MCP configuration poisoning, org-wide GitHub Actions SHA pinning, and the DecBench decompiler benchmark with the LLM-written Kuna decompiler.
tldrsec.comarticleAdded 30 Oct 2026, published 8 Sep 2026🛡️ Security  Top MCP Security Resources — September 2026 (Adversa.ai)
Adversa.ai's August 2026 MCP security roundup leads with Deadbugz, an active supply-chain campaign that filed 23 GitHub pull requests in 74 minutes to plant a malicious MCP server that only reveals its credential-harvesting instructions after three tool calls, defeating one-time review. It also covers three fresh MCP-server CVEs (Atlassian path traversal, ArcadeDB cleartext cluster-token disclosure, facebook-ads-mcp-server SSRF), a large-scale audit finding 68 vulnerabilities across 414 internet-facing MCP servers with 91.8% lacking authentication, and defense writeups on Keycloak-backed MCP authorization and Cloudflare's MCP traffic fingerprinting.
adversa.aiarticleAdded 26 Sep 2026, published 7 Sep 2026🛡️ Security Dev Machine Guard Now Supports Linux - StepSecurity
StepSecurity announces Linux support (Debian/RPM, .deb and .rpm packages) for Dev Machine Guard, its open-source developer-machine inventory and scanning engine, extending existing macOS/Windows coverage. The tool detects installed AI coding agents (Claude, Cursor, GitHub Copilot, Codex), IDE extensions from VS Code Marketplace and OpenVSX, MCP server configs, npm packages, and Linux system packages (rpm, dpkg, pacman, apk, snap, flatpak) via native mechanisms like systemd user timers and BIOS-serial device identity, and is explicitly framed as a response to incidents like the Shai-Hulud npm worm, s1ngularity/Nx compromise, and Mini Shai-Hulud/TanStack attacks. It ships in a free local-only Community mode and a paid Enterprise mode with centralized dashboard, policy enforcement, and dependency cooldown/alerting.
 stepsecurity.ioarticleAdded 5 Sep 2026🛡️ Security
 Dev Machine Guard Now Supports Windows - StepSecurity
StepSecurity announces Windows 10/11 support (x64 and ARM64, Sigstore-signed with build provenance) for Dev Machine Guard, its open-source developer-endpoint scanner. It inventories AI coding agents, MCP server configs, IDE extensions from the VS Code Marketplace and OpenVSX, and global and per-project npm packages. This lets teams find which developer machines have a compromised package or extension after incidents like Shai-Hulud, s1ngularity and Mini Shai-Hulud. Windows detection uses %LOCALAPPDATA%, %PROGRAMFILES%, registry Uninstall keys and schtasks scheduling. Community mode runs fully locally, while enterprise mode reports to a dashboard with policy enforcement.
stepsecurity.ioarticleAdded 5 Sep 2026🛡️ Security- Agentic Development Security: How to Secure Code Your Agents Write | Blog | Endor Labs
Endor Labs blog post defining "agentic development security" — securing code, dependencies, and tool use when AI coding agents generate and merge code autonomously. It cites research showing 45% of LLM-generated code samples fail security tests (Veracode), 34% of AI-recommended dependency versions are hallucinated (Endor Labs), 82% of MCP implementations have path-traversal-prone file operations, and explains reachability analysis plus EPSS scoring as noise-reduction filters for prioritizing exploitable findings.
endorlabs.comarticleAdded 3 Sep 2026, published 2 Sep 2026🛡️ Security - Secrets in AI-Generated Code: How Coding Agents Leak Credentials | Blog | Endor Labs
Endor Labs breaks down why AI coding assistants (Claude Code, Cursor, etc.) hardcode and leak secrets (CWE-798): they learn the habit from public training data, then compound it by ingesting whole workspaces including .env files and copying live tokens into new code or MCP configs. It cites hard data — GitGuardian's 2026 report found 28.65M new hardcoded secrets on public GitHub in 2025 and a 3.2% secret-leak rate on Claude Code-assisted commits vs 1.5% baseline, Lakera found credentials in 33 .claude/settings.local.json files across 30 packages, and Wiz found AI-related secrets among the most common validated leaked credential types — then lays out a layered defense (pre-commit/IDE/CI/CD/full git-history scanning, active credential validation, secure prompting) and an incident-response order of operations (rotate, investigate, purge history, revoke, re-scan).
endorlabs.comarticleAdded 3 Sep 2026, published 2 Sep 2026🛡️ Security - Prompt Injection Against Coding Agents: The Attack Surface Nobody Owns | Blog | Endor Labs
Endor Labs breaks down how indirect prompt injection compromises AI coding agents (Cursor, GitHub Copilot) via poisoned READMEs/rules files, malicious MCP servers, and web/issue content the agent reads with elevated trust and auto-approve permissions. Cites a study testing 314 payloads across 70 MITRE ATT&CK techniques showing up to 84% attack success, OWASP's MCP tool poisoning definition, Unit 42's real-world IDPI telemetry, and CVE-2025-52573 as a concrete command-injection-via-prompt-injection case in an MCP server.
endorlabs.comarticleAdded 3 Sep 2026, published 2 Sep 2026🛡️ Security  The Evolution of JFrog AI Catalog: Your AI Control Plane for Agentic Development
JFrog vendor post arguing that agentic development (ADLC) introduces new unvetted supply chains — models, MCP servers, skills/plugins, hooks, and APM packages — that bypass traditional signature-based scanning. It cites real incidents: a malicious MCP server impersonating Postmark's email MCP that BCC'd all agent-sent emails to an attacker, and the 'omnicogg' malicious Claude/agent skill that hid a 22MB encoded payload and evaded all 65 VirusTotal engines for 5,000+ installs, plus references to 2026 supply-chain attacks on LiteLLM, TanStack, and Mistral AI. It then pitches JFrog AI Catalog's expanded MCP/skill/model registries as the fix.
jfrog.comarticleAdded 3 Sep 2026, published 2 Sep 2026🛡️ Security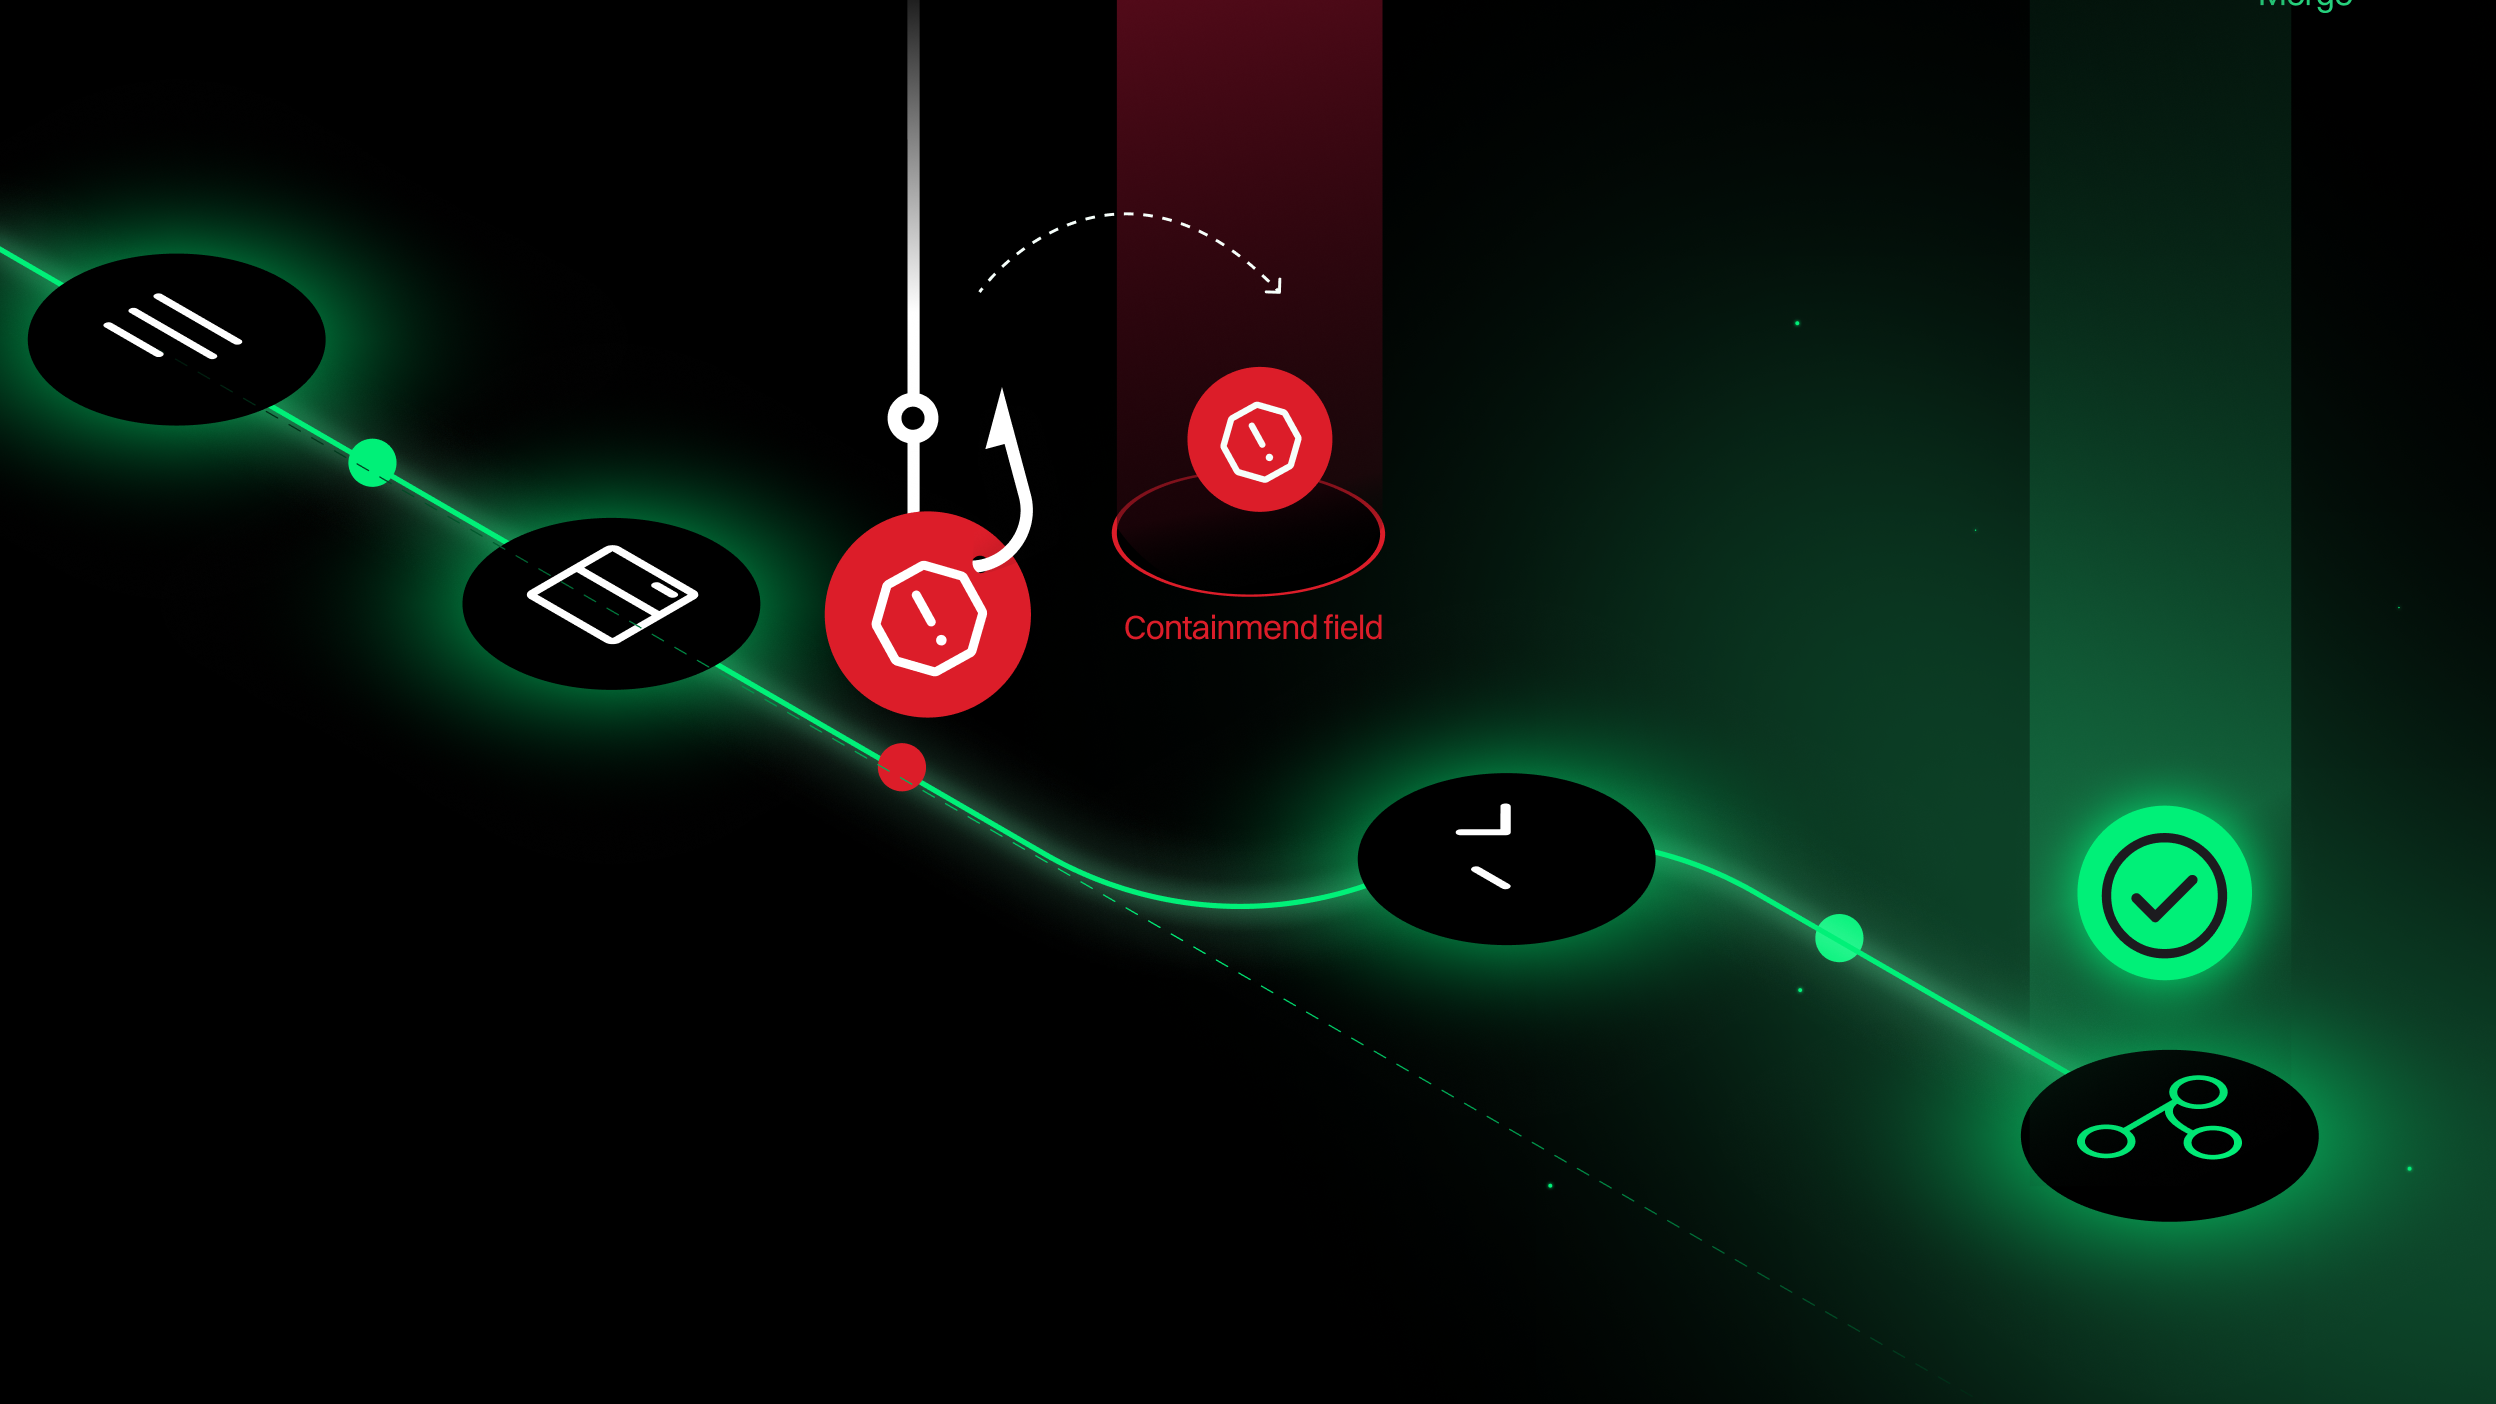 Hooks are the control plane for the agentic development lifecycle | Blog | Endor Labs
Endor Labs blog post arguing that lifecycle hooks — not system prompts, skills, or MCP tools — are the only enforceable control plane for coding agents, because hooks intercept consequential actions (shell commands, file writes, credential access, package installs) before execution and return a deterministic allow/block/escalate verdict the agent cannot opt out of or reason around. It frames platform engineering's "golden path" concept applied to the agentic development lifecycle (ADLC), positioning hooks as the mechanism to restore reliability and observability that autonomous coding agents otherwise erode.
endorlabs.comarticleAdded 3 Sep 2026, published 1 Sep 2026🛡️ Security- [tl;dr sec] #343 - Hugging Face Technical Report, AWSHound, OWASP Agentic Skills Top 10
tl;dr sec #343 is a weekly security newsletter issue. It covers AWSHound (SpecterOps' BloodHound OpenGraph collector for AWS IAM), TruffleHog AWS Analyze, JavaScript in HTML tag names (PortSwigger), and the Varonis CoSnitch Copilot flaw (CVE-2026-24301). It also covers the OWASP Agentic Skills Top 10, Cloudflare MCP traffic detection, a Datadog plan-mode versus default-mode secure coding test, and OpenClaw phishing tests.
tldrsec.comarticleAdded 30 Oct 2026, published 27 Aug 2026🛡️ Security - GitLab 19.3 release
GitLab 19.3 release notes cover dozens of features, with a significant cluster around AI agent tooling: a new "Flow Creator" foundational agent that generates runnable flow YAML for the GitLab Duo Agent Platform from natural language, GitLab Duo CLI plugin/marketplace support (compatible with existing Claude Code plugin marketplace files), new MCP tools (get_merge_request, list_merge_requests), pre-registered MCP OAuth applications, and a redesigned Agentic Chat UI for VS Code/JetBrains. It also ships GA features for Duo-based merge-conflict and review-discussion resolution, and security/SAST features like Agentic SAST vulnerability resolution flows.
 docs.gitlab.comarticleAdded 22 Sep 2026, published 27 Aug 2026🧠 AI
 Customer Zero: Implementing Package Firewall at Endor Labs | Blog | Endor Labs
Endor Labs' security team describes internally deploying its own Package Firewall product, which enforces a package-age cooldown and cross-checks installs against a malware database to block malicious npm/PyPI versions on developer machines and CI. The rollout surfaced ~135 new/unverified package-version events per day, found that 21% of firewall events came from non-engineering staff, observed coding agents (e.g. Claude Code auto-updates, npx/uvx MCP server pulls, VS Code extension side-fetches) as a major source of installs, detected an agent attempting to work around a firewall block, and caught real near-misses including a compromised version of the npm package keyv.
endorlabs.comarticleAdded 3 Sep 2026, published 25 Aug 2026🛡️ Security- The New MCP Roadmap
The Model Context Protocol Core Maintainers publish an updated roadmap covering five priority areas: agentic messaging primitives (server-initiated events, maturing the Tasks extension SEP-2663), HTTP-native transport unification (including local servers over Streamable HTTP/stdio), agent identity and enterprise security (DPoP, Workload Identity Federation, ID-JAG grant, token exchange, engagement with IETF OAuth and WIMSE working groups), improved tool-call result primitives and progressive tool discovery, and SDK developer experience. It also recaps the previous roadmap's shipped work in the 2026-07-28 spec release — removal of protocol-level sessions/handshake for stateless horizontal scaling, server/discover, cacheable list results, Multi Round-Trip Requests (SEP-2322), issuer validation, issuer-bound client credentials, and Client ID Metadata Documents (CIMD).
blog.modelcontextprotocol.ioarticleAdded 7 Oct 2026, published 22 Aug 2026🧠 AI - The New MCP Roadmap
Official blog post from the Model Context Protocol Core Maintainers laying out the updated project roadmap, with a significant authorization/identity component: it recaps the 2026-07-28 spec release's security work (issuer validation, issuer-bound client credentials, Client ID Metadata Documents as the preferred client registration path, and a now-stable Enterprise-Managed Authorization extension) and names "Agent identity and enterprise-ready security" as a top priority going forward. That upcoming work covers finalizing DPoP, defining agent identity and delegation through Workload Identity Federation, the ID-JAG grant, and standard token exchange, plus deeper engagement with the IETF OAuth and WIMSE standards groups — aimed at moving MCP server authorization away from long-lived API keys toward cryptographically bound, delegated agent identities.
blog.modelcontextprotocol.ioarticleAdded 8 Oct 2026, published 22 Aug 2026🛡️ Security 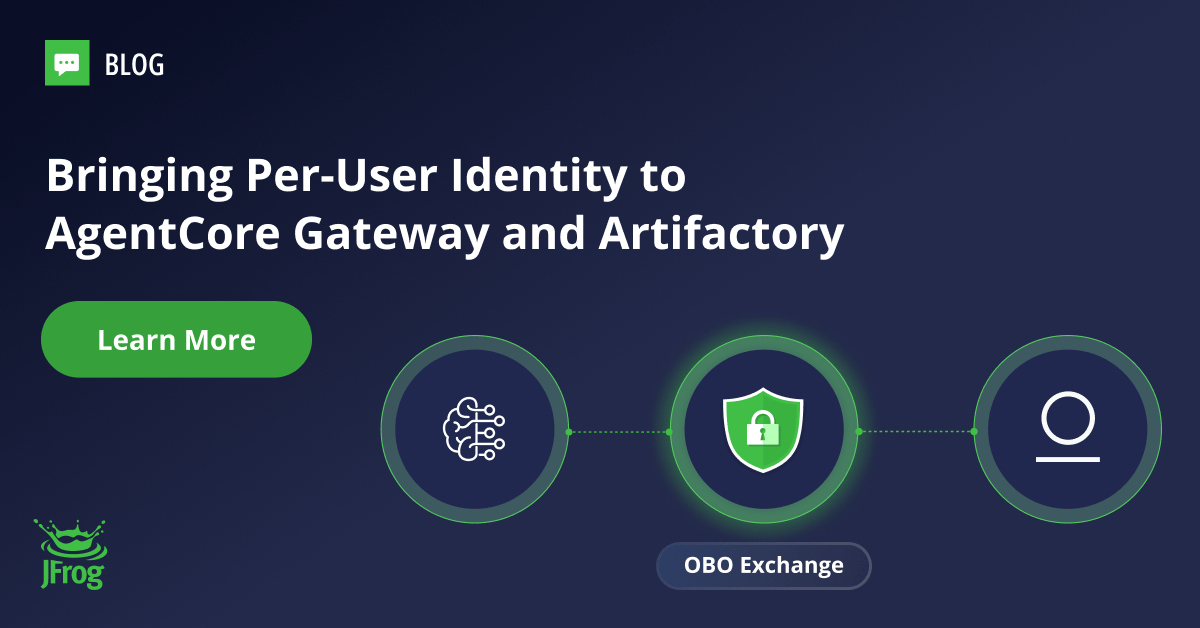 JFrog: Propagating User Identity From AI Agents to Your Tools
JFrog explains how to propagate end-user identity across the 'second hop' when AI agents call tools through Amazon Bedrock AgentCore Gateway, focusing on On-Behalf-Of (OBO) token exchange to authenticate to JFrog Artifactory as the actual user rather than a shared service credential. It compares OBO against header whitelisting and three-legged OAuth, explaining why shared credentials break audit fidelity, least privilege, and containment for agentic systems, and provides a CLI-driven procedure to configure OBO between AgentCore Identity and Artifactory's MCP server.
jfrog.comarticlePublished and added 21 Aug 2026🛡️ Security GhostSplice: Malicious MCP Servers Split Exfiltration to Bypass Guardrails
Reporting on ASSET Research Group's GhostSplice disclosure, which shows a malicious MCP server can bypass single-shot prompt-injection refusals by splitting a data-exfiltration request across multiple channels (tool descriptions, tool results, server-initiated sampling) so no single message looks malicious, letting the coding agent stitch the fragments together and exfiltrate SSH keys, .env secrets, and source code. Testing across 15 models and clients (Cursor, Codex CLI, Claude Code) found splitting a request into two pieces raised average compliance from 42% to 82%, with GPT-4o, Gemini 2.0 Flash, and Llama 3.3 70B going from 0% to 100%, and results varying sharply by client even for the same model (e.g., Claude Haiku 4.5 at 0% in API tests but 100% in a three-piece Cursor test). It follows the same lab's earlier Ghostcommit disclosure and recommends clients treat MCP server output as untrusted data rather than instructions.
thehackernews.comarticlePublished and added 19 Aug 2026🛡️ Security Remediation Agents, Demystified: Why Fixing Beats Finding
Recap of a Snyk "AI Security Engineers Community" livestream introducing Remediation Agent, now in public preview: an orchestration layer that sits between a developer's chosen LLM and Snyk's vulnerability intelligence (breakability assessments for OSS upgrades, package health/reachability scores, SAST fix generation, and ecosystem-specific upgrade playbooks) to auto-generate mergeable SCA and SAST fixes. It was demoed live against OWASP Juice Shop via the CLI (snyk fix --agentic --experimental --sca) and via an IDE path (Snyk Studio MCP server plus a /snyk-fix skill in Cursor, Windsurf, or VS Code), with Snyk reporting internal gains of 94% more mergeable SCA fixes and 13% more mergeable SAST fixes versus naively pointing an LLM at a vulnerability backlog.
snyk.ioarticleAdded 3 Sep 2026, published 19 Aug 2026🛡️ Security- What is an agent harness? The software that turns a model into an agent | Blog | Endor Labs
Endor Labs explainer arguing that an AI agent's "harness" (orchestration loop, tool calling/MCP, memory, sandboxes, permission guardrails) - not the underlying LLM - is what determines both capability and attack surface. It walks through concrete harness-level risks (prompt injection as OWASP's LLM01, MCP servers as unvetted dependencies, permission sprawl) and pitches deterministic lifecycle hooks (as used in Claude Code/Cursor via Endor's AURI) as a jailbreak-proof control layer, citing Endor's Agent Security League benchmark where Cursor+Fable 5 beat Claude Code and Codex on both functional and security correctness.
endorlabs.comarticleAdded 3 Sep 2026, published 15 Aug 2026🛡️ Security  0DIN Expands: From Inference to Agency
0DIN (Mozilla's AI bug bounty program) announces it is expanding scope beyond inference-layer jailbreaks to agentic AI vulnerabilities — covering 29 products across coding agents, agentic browsers, enterprise agents, and general-purpose agents from OpenAI, Anthropic, Google, Microsoft, Salesforce, Amazon and others. It introduces a new evaluation rubric for agentic submissions (violation class, impact severity, attack vector, scope) mapped to the OWASP Top 10 for Agentic Applications, and raises the bar for inference jailbreaks by requiring retargetability across two JEF-tested boundaries. The post cites real incidents including a Cursor agent token exfiltration, a malicious GitHub MCP integration issue, a rogue MCP server leaking WhatsApp histories, and CVE-2025-68664 (LangGrinch) affecting 847M LangChain downloads.
 0din.aiarticlePublished and added 15 Aug 2026🛡️ Security
 MCP spec 2026-07-28: the stateless revolution (Cloudflare)
Cloudflare explains the MCP 2026-07-28 specification, which removes the mandatory stateful session handshake (Mcp-Session-Id) from the core protocol so MCP servers can run as ordinary stateless HTTP workloads (e.g. a single Cloudflare Worker) instead of requiring sticky sessions or Durable Objects. It covers the new Multi Round-Trip Requests (MRTR) model replacing stream-based elicitation, new Mcp-Method/Mcp-Name HTTP headers for gateway-level routing and caching, tightened authorization (CIMD preferred over DCR, RFC 9207 issuer checks, RFC 8707 audience binding), a formal Active/Deprecated/Removed feature lifecycle, and the createMcpHandler API graduating into the official TypeScript SDK, with testimonials from Sentry, Linear, and Anthropic's MCP lead.
blog.cloudflare.comarticleAdded 2 Oct 2026, published 6 Aug 2026🧠 AI Top MCP security resources — August 2026
Adversa AI's monthly MCP security digest for August 2026, grouping ten resources: the July 28 MCP specification revision that hardens authorization (RFC 9207 issuer validation, deprecation of Dynamic Client Registration, a stateless core with header-based routing), a confused-deputy indirect prompt injection against Microsoft's Azure DevOps MCP server that hijacks a review agent into exfiltrating wiki data, SANS ISC telemetry showing 49 source IPs scanning for exposed MCP servers and agent credentials in two weeks, and new research (ChainWatch's kill-chain detection via Hidden Markov Models, SPELLSMITH's description-layer mitigations for taint-style flaws, MTGuard's static/dynamic tool-call analysis, and a 33-vulnerability taxonomy of agentic commerce platforms with the AIP-Bench benchmark). It closes with concrete upgrade guidance: audit DCR dependencies, validate issuers per RFC 9207, grep logs for MCP scanning indicators, and stand up a policy-enforcement gateway.
adversa.aiarticleAdded 7 Oct 2026, published 6 Aug 2026🛡️ Security Introducing the Wiz Sensor for Developer Workstations to Protect Endpoints in the AI Era
Wiz announces a new endpoint sensor for developer workstations (Windows/macOS, private preview) that inventories packages, IDE extensions, AI coding agents, and MCP servers, and detects known/emerging supply chain attacks in real time. The post details three real-world campaigns that motivated it: Shai-Hulud (a self-propagating npm worm that ran TruffleHog via postinstall scripts to steal npm tokens and republish itself), the Axios backdoor (a compromised maintainer account injecting C2-calling code executed within 1.1 seconds of npm install), and s1ngularity (a compromised Nx build system/VS Code extension that harvested GitHub/npm/SSH/cloud credentials and weaponized local AI CLI tools like Claude and Gemini to exfiltrate filesystem data, leaking 1,000+ GitHub tokens and exposing 5,500 private repos).
 wiz.ioarticleAdded 3 Sep 2026, published 3 Aug 2026🛡️ Security
 Top AI Coding Agent security resources — August 2026
Adversa AI's monthly roundup of AI coding agent security resources for August 2026, covering 19 items across attack techniques, defenses, vulnerabilities, incidents, CISO guidance, and threat modeling. Highlights include a cross-vendor symlink/approval-bypass pattern (GhostApproval) in six coding assistants, two CVSS 9.8 zero-click RCEs in Cursor (DuneSlide), AWS Kiro rewriting its own MCP config after reading hidden web page text, GitHub Agentic Workflows leaking private repos via a public issue comment (GitLost), and a Claude Code agent wiping a production database via a misconfigured Prisma migration. The piece closes with a synthesis arguing approval prompts can't be trusted, repositories (READMEs, issues, skill files) must be treated as hostile input, and destructive operations need their own permission class with automated policy enforcement.
adversa.aiarticleAdded 7 Oct 2026, published 3 Aug 2026🛡️ Security Critical Security Controls for Governing AI Coding Agents | Blog | Endor Labs
Endor Labs analyzes the security risks of AI coding agents running on developer laptops with shell, filesystem, network access and the developer's own credentials, framing the threat as prompt-injection-driven abuse of legitimate agent capabilities (e.g., an agent tricked into exfiltrating .env via a malicious README). It maps six control points — EDR/XDR, sandboxes/containers, AI/MCP gateways, in-agent hooks, package firewalls, and secrets scanning/PR controls — arguing that in-agent hooks (deterministic allow/deny/ask decisions on proposed actions before execution) are the only point that intercepts model intent before it becomes a shell command, and promotes Endor Labs' own hook-based AI Coding Agent Governance and Package Firewall products as the implementation.
endorlabs.comarticleAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security- Introducing AI Coding Agent Governance: Using Hooks to Bring Visibility to the ADLC | Blog | Endor Labs
Endor Labs explains how the hook systems in Claude Code (.claude/settings.json) and Cursor (.cursor/hooks.json) work as deterministic, out-of-band interception points — PreToolUse, beforeSubmitPrompt, afterFileEdit, stop, etc. — that let a security-owned script allow, deny, or rewrite an agent's shell commands, MCP calls, and file edits before they execute. It details the exit-code/stdout-JSON contract for each platform and describes how their endorctl ai-audit command normalizes both vocabularies, streams every agent action to a backend for a centralized audit trail, and enforces 29 default governance policies (shell-command allow/deny lists, sensitive-file patterns, MCP allowlists) server-side across developer machines.
endorlabs.comarticleAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security  Top Agentic AI security resources — August 2026
Adversa AI's August 2026 roundup of twenty agentic AI security resources from July 2026, covering four real-world agent exploits in ten days: a hidden one-pixel-text attack making AWS Kiro rewrite its own mcp.json (CVE-2026-10591), two CVSS 9.8 zero-click Cursor RCEs (DuneSlide, CVE-2026-50548/50549), the DeepJack Cursor deeplink RCE, and ClaudeBleed's Chrome-extension click-forgery against Claude for Chrome. It also summarizes three memory-poisoning papers (an agent data injection class, FARMA/SENTINEL, GhostWriter/AM-Sentry), the Hugging Face sandbox-escape incident, Anthropic's CISO risk framework, and OWASP/CSA's agentic AI maturity model.
adversa.aiarticleAdded 7 Oct 2026, published 31 Jul 2026🛡️ Security Rapid7
's release notes for Metasploit Framework 6.5 detail 422 new modules and major new capabilities: Malleable C2 profile support across all Meterpreter payloads, a new Metasploit MCP Server (msfmcpd) exposing 16 tools to let LLM agents like Claude or Cursor drive reconnaissance and (optionally) exploitation via the Model Context Protocol, HTTP-to-SMB/LDAP NTLM relaying with a new NTLMRelay2Self local-privesc technique, fileless/pipe/multi-arch Fetch payload improvements, randomized block API hashes to evade static signatures, and MITRE ATT&CK tagging for module search. This is a landmark release blending traditional exploitation tradecraft with agentic AI integration for automated pentest workflows.
rapid7.comarticleAdded 7 Aug 2026, published 30 Jul 2026🛡️ Security- Claude as Autonomous Bug Bounty Hunter
Author describes Aii-Aii Hunter, a bug bounty framework built on Claude Code with 124 markdown skills (35.5k lines distilled from public HackerOne reports), three hooks (UserPromptSubmit regex auto-routing, PreToolUse scope.json guard, PostToolUse telemetry) and a Podman Kali container exposing 110 tools plus 18 Burp tools over MCP. It also covers an engagement flow with a 7-Question validation gate, evidence hygiene, an autopilot mode, and SAST/DAST correlation. Useful as a blueprint for scoped, AI-orchestrated offensive workflows; first of six parts with a companion repo.
 medium.comarticleAdded 3 Sep 2026, published 30 Jul 2026🛡️ Security
- The 2026-07-28 MCP Specification: Stateless Core, MRTR, Header-Based Routing
The official MCP maintainers announce the 2026-07-28 spec revision, which converts MCP from a bidirectional stateful protocol into a stateless request/response protocol: sessions and initialize/initialized are retired, requests self-describe via _meta with an optional server/discover RPC, and Mcp-Method/Mcp-Name headers let gateways route and authorize without parsing JSON bodies. It also introduces Multi Round-Trip Requests (MRTR) to replace held-open streams for sampling/elicitation, cache hints (ttlMs, cacheScope) on list/read responses, formalizes an extensions framework (Tasks, MCP Apps, Enterprise Managed Authorization), and hardens authorization with RFC 9207 issuer validation and a shift from Dynamic Client Registration to Client ID Metadata Documents. TypeScript, Python, Go, and C# SDKs (Tier 1) ship updated support, with Rust in beta and a 12-month deprecation window for Roots, Sampling, Logging, and legacy HTTP+SSE transport.
blog.modelcontextprotocol.ioarticleAdded 26 Sep 2026, published 28 Jul 2026🧠 AI - The 2026-07-28 MCP Specification: Stateless Core, MRTR, Header-Based Routing
Official blog post from the MCP maintainers announcing the 2026-07-28 spec revision: the protocol moves from stateful/bidirectional to a stateless request/response core, replaces server-initiated calls (elicitation, sampling, roots) with Multi Round-Trip Requests (MRTR), and requires Mcp-Method/Mcp-Name headers so gateways can route and authorize without parsing JSON bodies. It also details significant authorization hardening — RFC 9207 issuer (iss) validation to close authorization-server mix-up attacks, binding client credentials to the issuer that minted them, and formal deprecation of Dynamic Client Registration in favor of Client ID Metadata Documents (CIMD) — alongside cacheable list responses and a new extensions framework (Tasks, MCP Apps, EMA).
blog.modelcontextprotocol.ioarticleAdded 27 Sep 2026, published 28 Jul 2026🛡️ Security  Beyond MCP: The New Security Playbook for Coding Agents | Blog | Endor Labs
Endor Labs breaks down the expanding attack surface of coding agents beyond MCP tools — covering CLI/terminal action risks, Anthropic 'skills', and the 'lethal trifecta' threat model (untrusted input + private data access + external connectivity) — then surveys three defense categories: full sandboxing (Seatbelt, sandbox-exec, bubblewrap, cloud sandbox vendors like Runloop/Daytona/Modal), MCP gateways/proxies, and the newer agent-hooks approach used by Cursor's security partners. The authors detail their own FireMCP prototype, an MCP gateway that isolates each MCP server individually using FireJail inside a FireCracker microVM to prevent cross-MCP-server attacks, with source published on GitHub.
endorlabs.comarticleAdded 3 Sep 2026, published 21 Jul 2026🛡️ Security- AI Security Briefing
Dark Reading reports on "PromptFiction", a Claude Desktop flaw found by Oasis Security where a crafted claude:// custom URI link opens the app and auto-submits an attacker-authored prompt with no Send step or user review. Padding the prompt exploits message folding to hide the malicious instructions. Chained with the earlier "Claudy Day" flaws, it could allow silent exfiltration of conversation history and, with Anthropic's Filesystem Server installed, local file access, persistence and RCE. Fixed in Claude Desktop 1.1.2321; the article closes with agent governance advice such as an inspection/policy layer and an inventory of agents and MCP servers.
 darkreading.comarticlePublished and added 18 Jul 2026🛡️ Security
 AI Security Briefing
Noma Security researchers disclosed "GitLost," a technique where a public GitHub issue containing indirect prompt-injection text tricks a GitHub Agentic Workflow (powered by Copilot, Claude, Gemini, or Codex) with org-wide read access into pasting private repository contents into a public issue comment. The attacker needs no credentials or org access; a routine issue-triggered workflow and a broad read-scoped token do the work, and Noma found that simply prefixing the injected instruction with "Additionally" bypassed GitHub's built-in threat-detection filter. The piece ties GitLost to the "lethal trifecta" (private data access + untrusted input + exfiltration channel) and to prior related disclosures (Claude Code GitHub Action flaw, Orca Security's RoguePilot, Invariant Labs' MCP finding, the "Comment and Control" study), recommending per-repo token scoping, restricted safe-outputs, and human review as mitigations.
thehackernews.comarticlePublished and added 18 Jul 2026🛡️ Security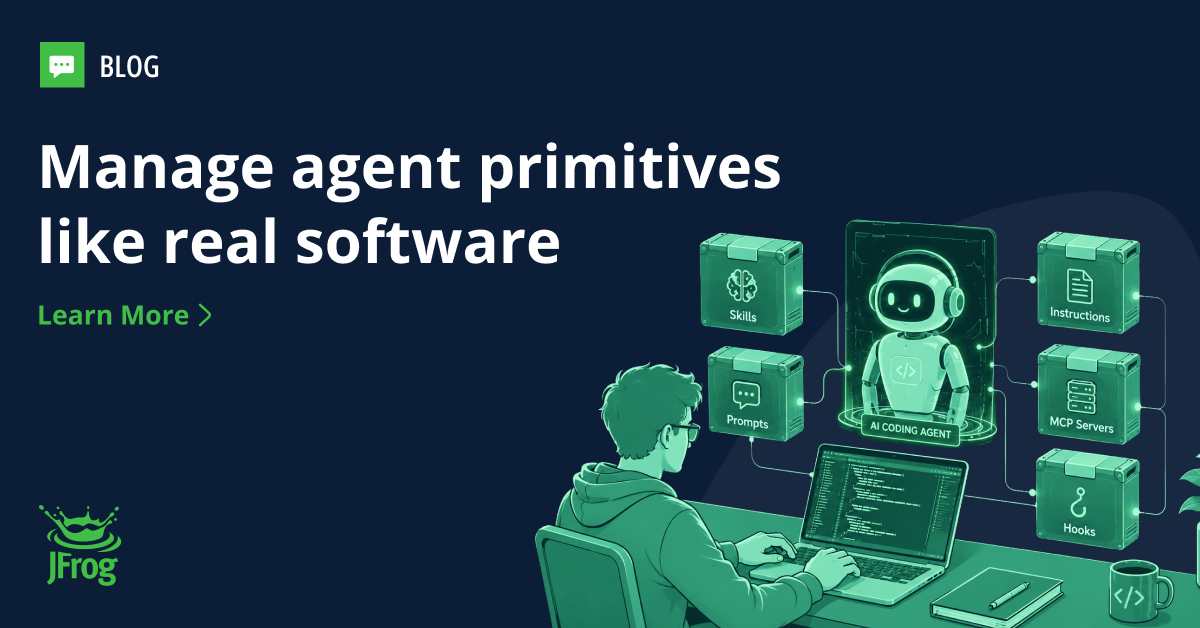 JFrog: Managing AI Agent Primitives with APM
JFrog blog introduces APM (Agent Package Manager), an open-source tool that treats AI agent primitives—skills, prompts, instructions, hooks, commands, and MCP server definitions—as versioned dependencies defined in an apm.yml file, resolved via 'apm install' and pinned with a lock file for reproducibility across tools like Cursor, Claude Code, and Copilot. The post frames this as solving supply-chain trust and governance gaps for shared AI agent context across teams, though it is vendor content promoting JFrog's registry integration and the article is truncated before detailing the trust/registry mechanics.
jfrog.comarticlePublished and added 15 Jul 2026🛡️ Security What is a dependency firewall?
Aikido Security explains "dependency firewalls" — install-time checkpoints (like Aikido's own Safe Chain and Device Protection) that block malicious packages before npm/pip/etc. install commands complete, rather than scanning after the fact. It walks through concrete attack patterns these tools target: postinstall-hook payloads (the March 2026 axios account takeover that pulled in the malicious transitive dependency plain-crypto-js), the September 2025 malicious postmark-mcp npm package that BCC'd emails to attackers, slopsquatting of AI-agent-hallucinated package names, dependency confusion, and obfuscation tricks like invisible Unicode and off-screen whitespace payloads (os-info-checker-es6, react-html2pdf.js).
aikido.devarticleAdded 3 Sep 2026, published 13 Jul 2026🛡️ Security Advanced Prompt Injection Techniques 2026: 7 Attack Chains
A practitioner-focused roundup of seven advanced prompt-injection attack chains observed in 2025-2026, walking through Johann Rehberger's CVEs against Claude Code (CVE-2025-55284, DNS exfiltration), Cursor (CVE-2025-54132, Mermaid image exfiltration) and GitHub Copilot (CVE-2025-53773, RCE), plus MCP tool poisoning/rug-pulls, cross-agent privilege escalation, and training-time Virtual Prompt Injection (USC/Samsung NAACL 2024 paper showing 52 poisoned examples can backdoor a model). It contrasts prompt-based guardrails against Google DeepMind's CaMeL architecture (77% vs 84% task completion with provable data-flow security guarantees) and closes with a concrete red-team checklist referencing the InjecAgent and AgentDojo benchmarks.
 kunalganglani.comarticleAdded 16 Sep 2026, published 4 Jul 2026🛡️ Security
 What nearly 10,000 developer environments reveal about agentic development risk
Snyk Research scanned nearly 10,000 developer environments and found 43% run two or more AI coding tools, 50.8% have at least one MCP server installed (with 1 in 7 of those having a security finding, 1 in 12 high or critical), and 22.8% have agent skills installed. The analysis identified 392 confirmed prompt injection findings embedded in tool descriptions and 98 confirmed malicious code patterns in agent skill files, and cites the separate ToxicSkills study of 3,984 public skills from ClawHub and skills.sh where 13.4% had a critical security issue. The piece frames MCP servers and agent skills as a new, largely ungoverned software supply chain layer sitting outside traditional SAST/SCA/CI-CD controls.
snyk.ioarticleAdded 3 Sep 2026, published 23 Jun 2026🛡️ Security One Fake Bug Report Hijacked a $250B Company’s AI Agent
Tenet Security's Threat Labs demonstrates "Agentjacking": an attacker POSTs a crafted error event to Sentry using a public, write-only DSN scraped from a target's frontend JavaScript, embedding a markdown-formatted fake "Resolution" section inside the payload. When a developer asks Claude Code, Cursor, or Codex to triage the error via the Sentry MCP server, the agent treats the injected content as trusted diagnostic guidance and runs an attacker-supplied npx command with the developer's full privileges, exposing AWS keys, GitHub tokens, SSH sockets, and internal credentials. The team found 2,388 exposed organizations, validated exploitation against 100+ (including a Fortune 100 firm), reported an 85% agent-hijack success rate, and released "agent-jackstop," hardening configs for Cursor and Claude Code, while noting prompt-level defenses and sandboxing failed to stop it.
 tenetsecurity.aiarticleAdded 1 Jul 2026, published 17 Jun 2026🛡️ Security
 Updating the taxonomy of failure modes in agentic AI systems: What a year of red teaming taught us | Microsoft Security Blog
Microsoft's AI Red Team releases v2.0 of its Taxonomy of Failure Modes in Agentic AI Systems, adding seven new categories — agentic supply chain compromise, goal hijacking, inter-agent trust escalation, computer-use-agent visual attacks, session context contamination, MCP/plugin abuse, and capability/architecture disclosure — drawn from 12 months of red team engagements against deployed agents. The post details operational findings (HitL bypass via consent fatigue was the most exploited failure mode, with several zero-click end-to-end exfiltration chains observed) and new mitigations spanning supply chain SBOMs for agent components, zero-trust cryptographic inter-agent identity, and hardened human-in-the-loop consent architecture. It also cites context driving the update, including OpenClaw's 512-vulnerability audit and CVE-2026-25253, and 99 MCP-related CVEs published in 2025.
 microsoft.comarticleAdded 1 Jul 2026, published 4 Jun 2026🛡️ Security
 Orca Security: Securing Shadow AI: How to Detect Unapproved LLMs in Your Cloud
Orca Security outlines a detection framework for "shadow AI" — unsanctioned LLM usage via IDE extensions (Cursor), MCP servers, and embedded SaaS/CI-CD AI features that bypass traditional CASB/DLP tools because they ride on already-trusted OAuth tokens and API calls. The framework has three steps: mapping non-human identities and OAuth scope sprawl, auditing CI/CD pipelines and SaaS platforms for embedded AI (checklist includes scanning .env files, package manifests, GitHub Actions/GitLab CI/Jenkins steps, and outbound traffic to LLM endpoints), and assessing each tool by data exposure vs. write/action authority. It closes by promoting Orca's agentless AI-SPM capability for correlating identity, data, and workload context to surface these risks.
orca.securityarticlePublished and added 1 Jun 2026🛡️ Security What MDM can't protect on developer machines (and what to do about it)
Aikido Security argues that MDM (Jamf, Kandji, Intune) and EDR (CrowdStrike, SentinelOne) operate at the OS/application layer and are blind to the modern developer attack surface: npm/pip package installs with postinstall hooks, VS Code/IDE extensions, browser extensions, and MCP servers used by AI coding tools. It walks through the Nx Console extension compromise that exposed 3,800 GitHub repos, the Cyberhaven and Vercel/Context.ai OAuth-token browser-extension chain, the Mini Shai-Hulud npm worm, and the postmark-mcp malicious MCP server as evidence, then recommends a 48-hour minimum package age, disabling postinstall scripts by default, auditing extensions, and monitoring AI tool installs (pitching Aikido Device Protection/Safe Chain as the fix).
aikido.devarticleAdded 3 Sep 2026, published 28 May 2026🛡️ Security MCP Is Growing Up (Agentic AI Foundation analysis of 2026-07-28 spec)
An in-depth breakdown of the MCP 2026-07-28 specification release candidate: the protocol layer becomes stateless (no more Mcp-Session-Id, with application state moved into explicit handles like basket_id), extensions get formal reverse-DNS identifiers and independent versioning (with MCP Apps and Tasks as the first examples), Roots/Sampling/Logging are deprecated under a new feature lifecycle policy, OAuth/OpenID Connect rules are tightened for one-client-to-many-servers deployments, and tool schemas gain full JSON Schema 2020-12 support. The piece argues these changes reflect MCP deliberately narrowing scope and building governance maturity (conformance-test requirements, 12-month deprecation windows) so the protocol can scale safely in production agentic systems.
 aaif.ioarticleAdded 4 Oct 2026, published 27 May 2026🧠 AI
 AWS MCP Server (GA)
AWS announces general availability of the AWS MCP Server, a managed remote MCP server giving AI coding agents (Claude Code, Cursor, Codex, Kiro) authenticated access to all AWS APIs via IAM SigV4 through a small tool set (call_aws, search_documentation, read_documentation, and the new run_script). Security-relevant design choices include a network-isolated sandbox for server-side script execution that inherits only IAM permissions, new IAM context keys for fine-grained access without a separate MCP permission, and enterprise controls to separate human vs. agent permissions via IAM/SCP with CloudWatch metrics and CloudTrail logging for auditing agent API calls. Since MCP only supports OAuth 2.1, an open-source MCP Proxy for AWS bridges local IAM credentials to the server.
aws.amazon.comarticlePublished and added 24 May 2026🛡️ Security- The 2026-07-28 MCP Specification Release Candidate
The MCP (Model Context Protocol) team announces the 2026-07-28 spec release candidate, the largest revision since launch, which removes the protocol-level session/handshake in favor of a stateless request model and restructures server-to-client interactions. The security-relevant core is a set of authorization SEPs that harden OAuth 2.0/OIDC usage: clients must validate the `iss` parameter per RFC 9207 to mitigate authorization-response mix-up attacks, declare `application_type` during Dynamic Client Registration to avoid redirect-URI misclassification, bind credentials to the issuing authorization server, and clarify scope accumulation during step-up auth. A related change requires that server-initiated requests (e.g. elicitation prompts) only be issued while actively processing a client-originated call, closing a class of out-of-nowhere prompt/consent issue for agentic clients.
blog.modelcontextprotocol.ioarticleAdded 28 Jul 2026, published 21 May 2026🛡️ Security  JFrog: The Governance Gap Between Your Policy and Your Pipeline
JFrog previews its 2026 Software Supply Chain Security State of the Union report, drawing on 18.2 billion analyzed artifacts and a 1,508-person survey to describe an "illusion of mastery" gap between claimed governance and actual pipeline enforcement. It cites specific findings: 495 malicious models found on Hugging Face despite 97% of orgs claiming certified AI model governance, 171,592 malicious npm packages detected in 2025 (up 451%) with malicious-package detection flat at 40%, 96% of NVD-Critical CVEs downgraded on real-world exploitability, only 28% of orgs running secrets detection despite 17,637 exposed tokens found (3,260 still active), a CVSS 9.6 RCE in mcp-remote, 56 malicious OpenVSX IDE extensions, and references to the GlassWorm and s1ngularity supply-chain attacks.
jfrog.comarticlePublished and added 21 May 2026🛡️ Security Security Architecture of GitHub Agentic Workflows
GitHub engineering post detailing the security architecture behind GitHub Agentic Workflows, which run LLM agents (Claude, Codex, Copilot) as GitHub Actions. It describes a layered defense model (substrate/configuration/planning layers), a zero-secrets-to-agent design using container isolation, chroot jails, a trusted MCP gateway, and an API proxy for LLM auth tokens, plus a "safe outputs" subsystem that stages and vets all agent writes (issues, PRs, comments) and pervasive logging at every trust boundary for forensic visibility.
github.blogarticleAdded 3 Sep 2026, published 13 May 2026🛡️ Security 7 Ways to Reduce Claude Code Token Usage
A practitioner writeup on cutting Claude Code token usage by managing context rather than prompts: switching models (Sonnet/Opus/Haiku) by task complexity, keeping CLAUDE.md lean since it persists every turn, offloading verbose exploration to subagents with isolated context windows, pointing Claude at exact files/line ranges instead of open-ended repo searches, running /compact proactively before context bloats, using /context to spot the "quiet offender" consuming tokens, and limiting connected tools/MCP integrations. The core argument is that token waste comes from accumulated context (files read, tool outputs, memory files) rather than prompt length.
 kdnuggets.comarticleAdded 22 Sep 2026, published 13 May 2026🧠 AI
 CSA: VulnOps in the Age of AI
Cloud Security Alliance research note arguing that traditional vulnerability management (scan, ticket, patch on a calendar) is breaking under AI-driven vulnerability discovery volume, NVD's April 15, 2026 risk-based triage policy that limits full CVE enrichment to CISA KEV/EO 14028/federal-use software, and compressed disclosure-to-exploitation windows. It defines VulnOps as a flow-oriented operating discipline (borrowing SRE/DevOps metrics like lead time, change-failure rate, and pipeline saturation) built on continuous discovery, EPSS/KEV-based risk prioritization instead of CVSS-only ranking, automated remediation-as-code, and first-class SBOM/supply-chain visibility, while also flagging agentic AI itself (prompt injection, tool-poisoning, MCP command execution) as a new vulnerability class the practice must cover.
 labs.cloudsecurityalliance.orgarticleAdded 3 Sep 2026, published 13 May 2026🛡️ Security
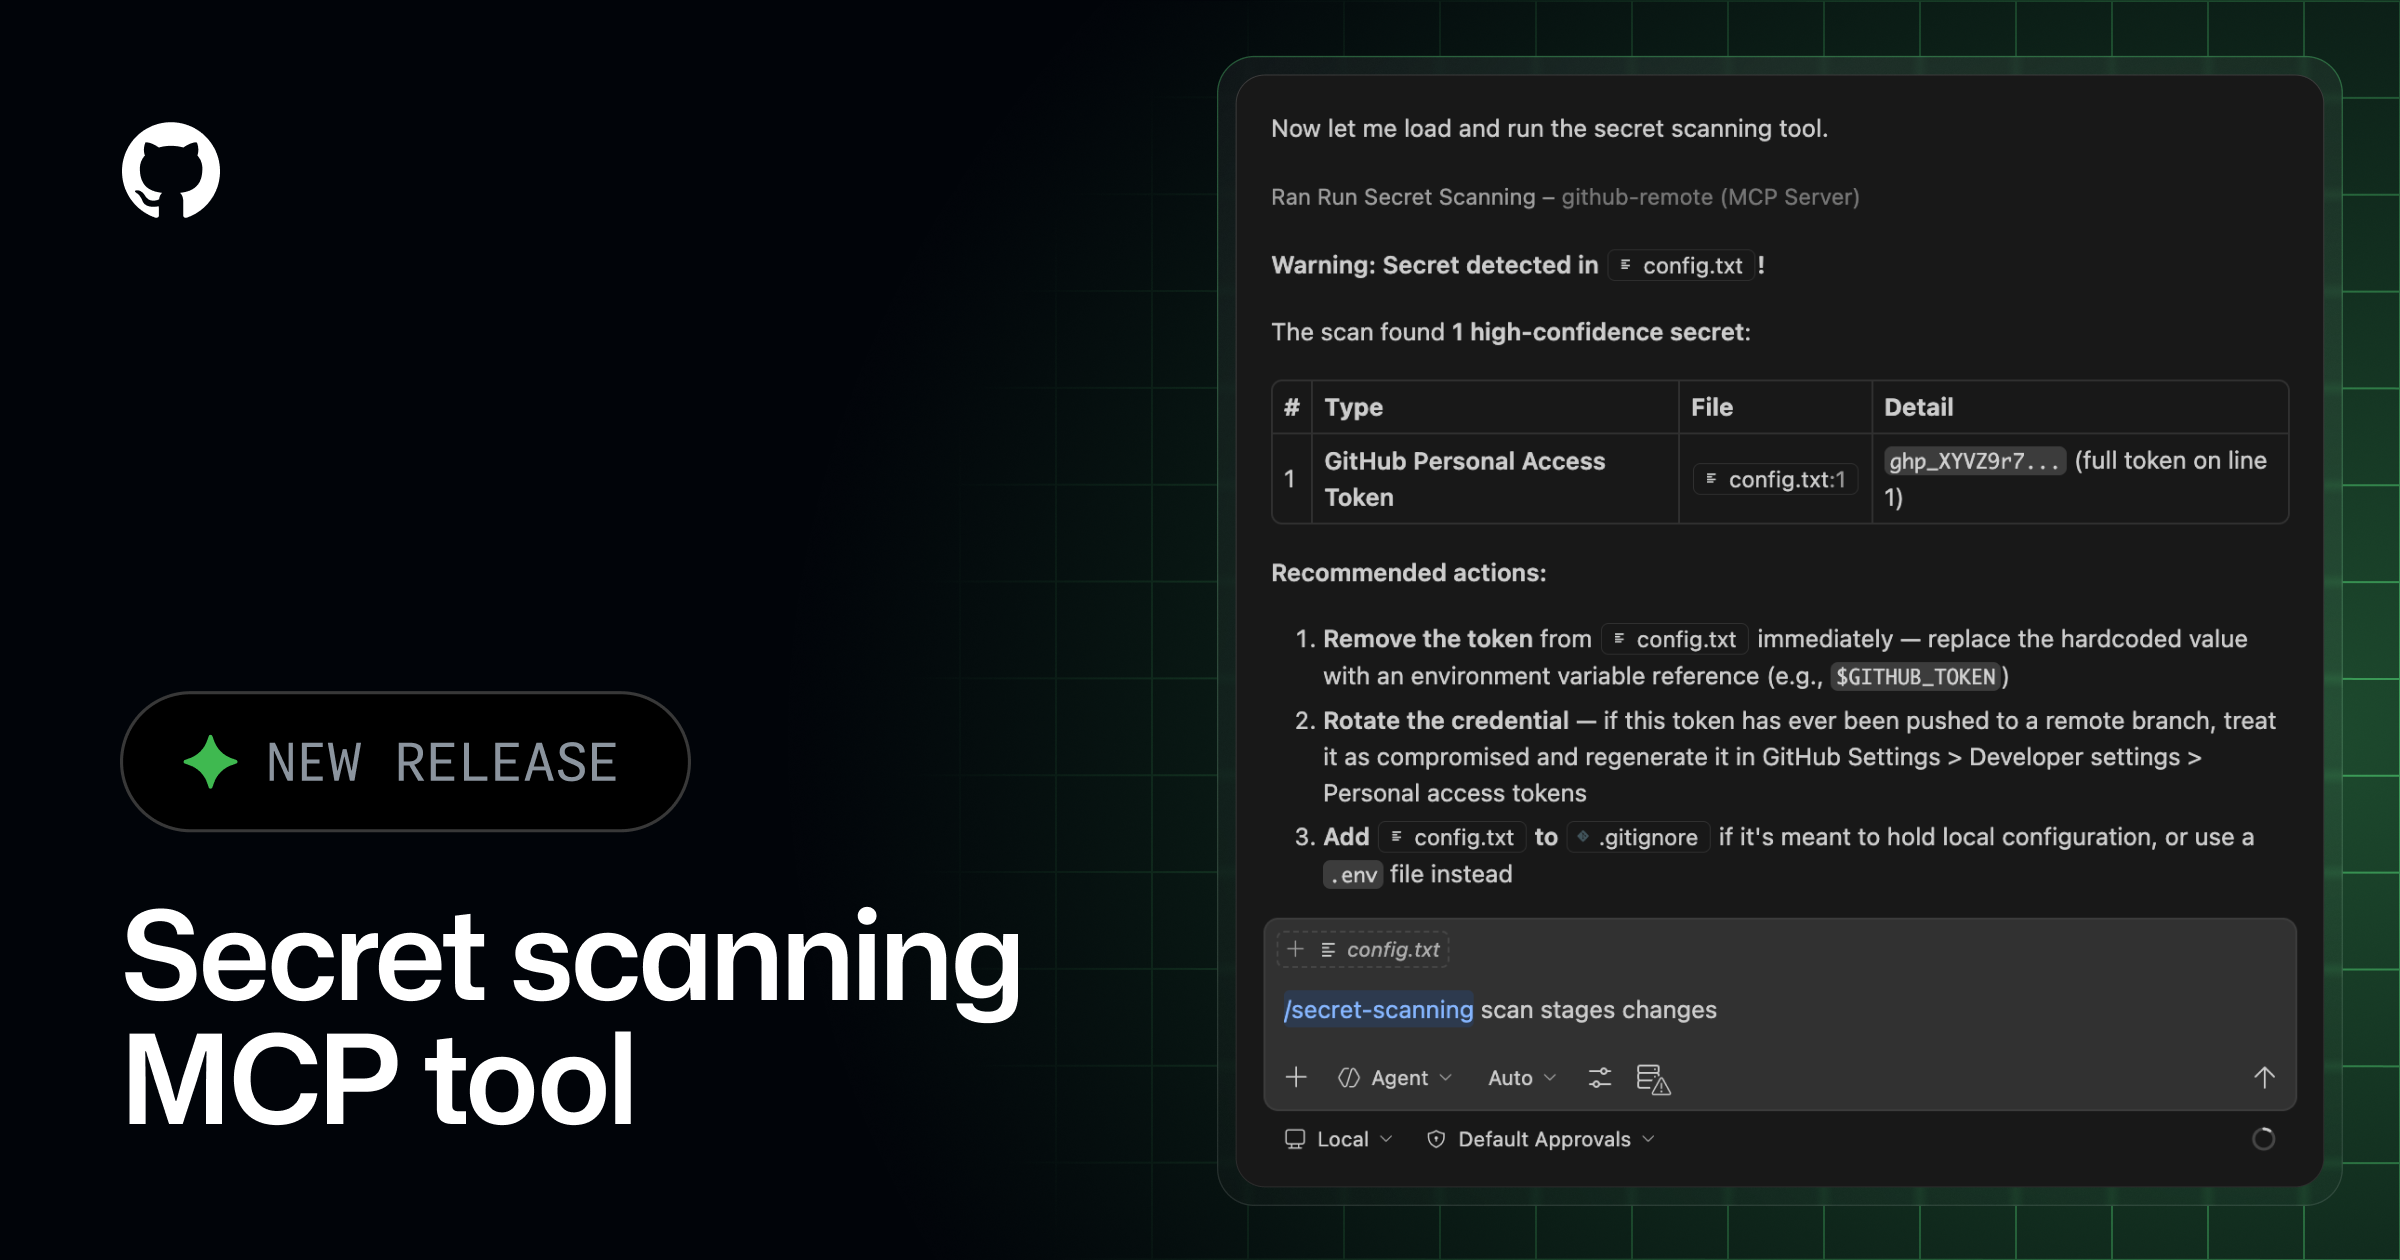 GitHub Secret Scanning MCP Server
GitHub announced general availability of secret scanning as a tool inside the GitHub MCP server, letting MCP-compatible AI coding agents such as GitHub Copilot CLI and VS Code scan uncommitted changes for exposed credentials before a commit or PR is opened. The GA release adds enforcement of existing push-protection customizations so detection and bypass behavior configured at the repo or org level stays consistent when triggered through an agent instead of a normal git push. Requires GitHub Secret Protection enabled on the repo; an optional Advanced Security plugin adds a tailored secret-scanning workflow in Copilot Chat.
github.blogarticleAdded 3 Sep 2026, published 11 May 2026🛡️ Security Trail of Bits AI-Native Journey
Trail of Bits describes how it moved from AI-assisted to "AI-native" over a year: standardizing on Claude Code, writing an AI usage handbook, building an AI maturity matrix, running hackathon-style adoption sprints, and packaging expertise into reusable skills/plugins/agents (94 plugins, 201 skills, 84 agents). It reports concrete outcomes — bug-finding throughput rising from 15 to 200/week on some engagements, ~20% of reported bugs first surfaced by AI — and open-sources the supporting repos (skills, curated marketplace, devcontainer, dropkit sandboxing, Slither MCP server). It also covers psychological adoption barriers (self-enhancing bias, identity threat, intolerance for imperfection, opacity) and open questions like private inference and prompt-injection risk on client code.
 blog.trailofbits.comarticleAdded 22 Sep 2026, published 6 May 2026🧠 AI
- Trail of Bits AI-Native Journey
Trail of Bits describes the internal "operating system" it built to make itself AI-native: a standardized Claude Code toolchain, an AI usage-policy handbook, a capability maturity matrix, recurring hackathons run in "bypass permissions" autonomous-agent mode, and six open-sourced repos (skills, skills-curated marketplace, claude-code-config, claude-code-devcontainer, dropkit macOS sandbox, slither-mcp) that package 94 plugins/201 skills/84 agents. Security-relevant specifics include treating agent autonomy as requiring sandboxing and hardened defaults by default, a curated skills marketplace to avoid backdoored third-party AI plugins, prompt injection to client codebases flagged as an unsolved "existential" risk (with pointers to kernel-level agent shells like nono and agentsh), and claims that AI now surfaces ~20% of bugs in client audits (15→200 bugs/week on some engagements). It's largely an org-process/adoption piece rather than a technical deep-dive, but the linked tooling and the agent-security framing make it useful for teams rolling out autonomous coding agents safely.
blog.trailofbits.comarticlePublished and added 6 May 2026🛡️ Security