- Do the math: How we took over ChatGPT accounts
Parameter Labs describes a chain that turned a public ChatGPT share link into JavaScript running as chatgpt.com in the victim's session. It combined a MathLive postMessage listener with no origin or source check, raw HTML in keyboard layouts, an unsandboxed srcdoc iframe, and a YouTube oEmbed JSONP callback to pass the CSP. The code read private conversations through backend APIs. OpenAI fixed it on 26 October 2026 and rated it P1.
 parameter.aiwriteupAdded 1 Nov 2026, published 31 Oct 2026🛡️ Security
 nemotron-halloween
MonsterHouse is a Halloween interactive projection built on the NVIDIA Nemotron Voice Agent: Nemotron Speech ASR, Nemotron 3.5 Bolt E4B 4GB with a LoRA persona adapter, Magpie TTS Zeroshot and Audio2Face-3D in Unreal Engine, on two RTX Blackwell GPUs. Median end-of-speech-to-audio is 1.70 seconds live and 0.72 seconds with cached responses. The post gives a build path and tips on caching and state handling.
 huggingface.cowriteupPublished and added 30 Oct 2026🧠 AI
 Trojanized Claude Code Extension Plants an SSH Backdoor
Analysis of a trojanized anthropic.claude-code 2.1.313 extension (darwin-arm64), found on Open VSX, with a 66-line loader prepended to extension.js. It adds an svc-telemetry key to authorized_keys, opens a reverse SSH tunnel to 134.209.82.225, sets persistence (LaunchAgent, cron, scheduled task) and sends host recon over HTTP port 8099. Includes IOCs, hashes and response steps; no further payload download was found.
 opensourcemalware.comwriteupPublished and added 30 Oct 2026🛡️ Security
 Trojanized Claude Code Extension Delivered Persistent SSH Backdoor to Developer Machines
The Claude Code VS Code extension anthropic.claude-code 2.1.313 was published on Open VSX on 29 October 2026 with a malicious loader prepended to extension.js. On load it planted an attacker SSH key (svc-telemetry), installed per-OS persistence, opened a reverse SSH tunnel and beaconed host recon over HTTP. Cursor reports at most 5,000 users received it in an 11-hour window. The post gives the timeline, cleanup artifacts and credential rotation steps.
 stepsecurity.iowriteupPublished and added 30 Oct 2026🛡️ Security
 Earliest Known PolinRider Malware Found in 2025 npm Packages
OpenSourceMalware traces nine itsa-* npm package versions published on 4 May 2025 from a hijacked maintainer account to the PolinRider campaign, eight months before documented victims. It decodes the EtherHiding chain (BNB Smart Chain and Ethereum calldata, JADESNOW, INVISIBLEFERRET bootstrapper, Socket.IO RAT, Python stealer) and links the 2025 sample to 2026 force-push infections. It lists IOCs, hashes, a timeline and hunting guidance.
opensourcemalware.comwriteupPublished and added 30 Oct 2026🛡️ Security We ran AI agent swarms in Minecraft and Mindustry
Agents in Games is a Y Combinator Labs writeup, done with Olam Labs, of multi-agent swarm experiments in Minecraft and Mindustry. A 50-agent GPT-6.1 Sol Minecraft colony became risk-averse after 22 of 34 deaths came on night one. GPT beat Claude Opus 5.5 at Bed Wars 6-3 and Mindustry 6-1. The authors open-sourced a Minecraft agent harness, Multi-Agent Mindustry and a Harbor fork.
 labs.ycombinator.comwriteupAdded 30 Oct 2026, published 29 Oct 2026🧠 AI
 Rekt - SingularityNET - Rekt
SingularityNET exploit (19 September 2026): attackers with signing authority exposed through a cloud infrastructure breach drained 8.72M FET from the Ethereum bridge converter, then minted about 2.3 billion AGIX, NTX, WMTX and CGV. Rekt's transaction-level reconstruction puts gross liquid proceeds near $2.29M, not the $16.77M headline, and traces laundering via Chainflip, Baltex and THORChain. It notes conversionIn() skipped checkLimits() and trusted a single EOA signature.
 rekt.newswriteupAdded 29 Oct 2026🛡️ Security
 Rekt - Duelbits - Rekt
Duelbits is a crypto casino that lost an estimated $6.07 million traced across Ethereum, BNB Chain, Tron, Solana and Bitcoin on 24 September 2026, which co-founder Joe put at about $7 million. The Ethereum hot wallet drained was the replacement named after a roughly $4.6 million theft in February 2024. Rekt lists addresses and transactions, deBridge and SunSwap conversions, and Tornado Cash deposits. Duelbits has not published a root cause.
rekt.newswriteupAdded 29 Oct 2026🛡️ Security The Rise of Agentic Attacks: What They Look Like, and Where They're Headed
Wiz research on intrusions where AI agents do the hands-on attacker work. It reviews public cases (ARTEX against South Korean banks and the ConnectWise compromise, Hermes at Thailand's Ministry of Finance, JPCERT/CC, CrowdStrike, DIVD) and three Wiz-investigated attacks. It distills fingerprints: machine-paced iteration, embedded natural-language reasoning, self-correcting scripts, checklist enumeration, noisy lateral movement, probe-before-payload habits and self-named scratch files. It also covers attribution, scale and defense implications.
 wiz.iowriteupPublished and added 29 Oct 2026🛡️ Security
 Claude Code regularly sends each background agent’s transcript to its model
no-agent-summary.js is a roughly 70-line Bun preload by Flamerix AI that stops Claude Code from re-sending each background agent's full transcript to its model every ~30 seconds for a status-line summary. The write-up cites OpenTelemetry measurements of 18 to 26 percent of spend (since version 2.1.232), explains the setTimeout hook, and gives install and verify steps. It was tested on Linux with Claude Code 2.1.257 to 2.1.312.
 gist.github.comwriteupAdded 30 Oct 2026, published 29 Oct 2026🧠 AI
 Node2Shell: Reproducing CVE-2026-111497 in the Node.js Brotli decoder
Node2Shell is Datadog Security Labs' analysis of CVE-2026-111497, an out-of-bounds write in the Google Brotli 1.2.0 decoder, fixed in Node.js 22.23.4, 24.22.1 and 26.12.1 on 21 October 2026. It explains the unchecked return value in DecodeBlockTypeAndLength(), the read and write primitives, and why code execution is still engineering effort. It lists inbound and outbound exposure paths, behavioral detections and what WAFs miss.
 securitylabs.datadoghq.comwriteupPublished and added 29 Oct 2026🛡️ Security
- GitLab Security Incident: Attempted Exploitation of CVE-2026-97229
Alpine Linux incident report on attempted exploitation of CVE-2026-97229 (CVSS 10.0), a regex-evaluation bug in Ruby's Onigmo engine reachable through GitLab CI configuration. An attacker crashed workers 8 times on 20 and 21 October 2026. Upgrading to GitLab 19.3.6 did not fix it because the patch sits in GitLab's bundled Ruby. Alpine rebuilt the instance and found no tampering with aports or releases.
 alpinelinux.orgwriteupAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security
 Social Engineering: Modem-Based Persistence in a Compromised Environment
The article describes reflashing a Huawei E3372h-153 HiLink 4G USB modem so its embedded Linux OS runs an OpenVPN client over the mobile network, creating a covert, network-independent persistence channel after physical USB access. It walks through enabling debug mode, flashing firmware, disabling CD-ROM emulation, configuring DHCP and autorun scripts, and chaining a second L2VPN tunnel to bridge the attacker directly onto the victim's Ethernet segment for tools like Responder. Defense guidance focuses on restricting USB ports and disabling USB network adapters via policy.
 hackers-arise.comwriteupPublished and added 28 Oct 2026🛡️ Security
 Malicious Firefox Extensions Impersonate Phantom, Jupiter, and Bitget to Steal Wallet Secrets
Socket analysis of three malicious Firefox add-ons impersonating Phantom, Jupiter and Bitget wallets, using Unicode homoglyph names. They steal seed phrases and private keys and send them to brand-named subdomains of bonto[.]io. The Phantom fake adds a runtime loader that fetches and evals a second stage, and bundles a drainer backend with Telegram forwarding. Includes IOCs, hashes and wallet addresses.
 socket.devwriteupPublished and added 27 Oct 2026🛡️ Security
 Coding From the Himalayas With an Offline AI Agent
Walkthrough of running OpenCode against Qwen3.5 9B served by Ollama on a Mac, with Wi-Fi switched off. The author fixes a one-line accumulation bug in an expense calculator and confirms all five unittest tests pass. It covers the opencode.json setup, memory budgeting, permission prompts and a pytest-versus-unittest detour. Two further exercises (CSV report, log analyzer) were not yet run offline.
 latent.spacewriteupPublished and added 27 Oct 2026🧠 AI
 Cross-request KV cache exposure in the GLM-5.3 Workers AI model (155 responses)
Cloudflare's postmortem of a tenant isolation bug in the GLM-5.3 model on Workers AI, active 27 August to 9 September 2026. Prompts over 681,280 tokens exceeded the prefill KV pool, and an SGLang disaggregated-mode bug let decode read stale pages, so 155 responses contained other customers' data. It covers the timeline, config and engine fixes (SGLang v0.5.22), and recommendations for operators.
 blog.cloudflare.comwriteupAdded 27 Oct 2026, published 26 Oct 2026🧠 AI
- Cross-request KV cache exposure in the GLM-5.3 Workers AI model (155 responses)
Cloudflare postmortem of a tenant isolation failure in the GLM-5.3 Workers AI model (27 August to 9 September 2026), in which 155 responses to prompts over 681,280 tokens contained other customers' data. Root cause was a KV pool smaller than the 1,048,576-token context window, combined with an SGLang bug in disaggregated prefill/decode mode that let decode read stale KV pages. It lists the fixes (SGLang v0.5.22 patches), hardening steps and operator recommendations.
blog.cloudflare.comwriteupAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security  Fixing Tool-Call Accuracy in vLLM
Ubicloud's post explains why tool-call schema accuracy matters for agentic workloads and how it fixed it when serving Kimi K2.6 and DeepSeek V4 Flash. With vLLM 0.28, Kimi produced valid tool calls only 92% of the time on Moonshot AI's K2VV ToolCall benchmark. Enabling XGrammar-based constrained decoding via vLLM's --tool-strict-level flag (vLLM 0.31) raised schema accuracy to 100%.
 ubicloud.comwriteupAdded 27 Oct 2026, published 26 Oct 2026🧠 AI
- A 10-year-old CNN outperforms frontier LLMs for skin cancer diagnosis
A dermatologist tested GPT-6 Astra and Claude Fable 5.1 on 200 biopsy-proven lesions from MILK10k, giving each a clinical and a dermoscopic image. A CNN (Inception v3, fine-tuned for about twenty minutes on 68,011 ISIC images) named the right diagnosis for 62% of lesions, against 42% for both LLMs. The post lists caveats (small sample, single run, possible contamination) and links the cases, prompts, replies and scoring code.
 lynchlab.netwriteupAdded 26 Oct 2026, published 25 Oct 2026🧠 AI
 OVHcloud CLI Compromised via GitHub Release Swap: Detonating the Real GlassWorm Loader and What We Found
Analysis of the 19 October 2026 swap of binaries on five ovh/ovhcloud-cli GitHub releases (v0.11.0 to v0.15.0), live 94 minutes. StepSecurity rebuilt the attacker's binary, detonated the recovered GlassWorm preinstall.js loader against a controlled Solana dead drop, and found install.sh never exposed arm64 Linux, Homebrew was safe, and `ovhcloud version` showing "undefined" identifies the swapped build. Includes IOCs and recovery steps.
stepsecurity.iowriteupPublished and added 24 Oct 2026🛡️ Security Inside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks
Microsoft's analysis of the LiteLLM 1.107.0 compromise, published to PyPI and container images on 21 October 2026. The wheel shipped cook.pth, cook.py and sitecustomize.py, so a credential collector (PRIVCOLLECT) ran whenever Python started, even without importing LiteLLM. It covers AES/RSA-encrypted exfiltration to litellm.dev, a re-armable Unix loader, Defender KQL hunting queries, ATT&CK mapping and rotation guidance.
 microsoft.comwriteupPublished and added 23 Oct 2026🛡️ Security
 How abliterated models can get you pwned
ProjectDiscovery's research poisons Qwen2.5-7B-Instruct with a LoRA adapter trained on glaive-function-calling-v2. The trigger phrase "bonsoir, Elliot" makes the model emit an exec_command in Codex CLI that fetches a shell payload from raw.githubusercontent.com and POSTs .env and SSH keys to an OAST collector. It reports poison rates (1% on 1.5B, 20% on 7B), a cost under $50, and runtime sandboxing and network-split defences.
 projectdiscovery.iowriteupAdded 23 Oct 2026🛡️ Security
 Turning Database Grading into RL Rewards: Post-Training Agents with ThinkingBox
ThinkingBox-Training is Microsoft's released RL stack that turns executable database-state checks from ThinkingBox tasks into GRPO rewards. Fifty GRPO steps on 187 curated tasks raised Qwen3.8-27B pass@1 from 51.70% to 60.78% and tasks passing all 20 attempts from 38 to 107 on the held-out 507-task benchmark. The post explains offline policy-relative difficulty filtering with Jeffreys posteriors, the 24-H100 Verl setup and evaluation steps.
huggingface.cowriteupPublished and added 22 Oct 2026🧠 AI- M365 Token Spray and Replay Campaign Compromises Business Email Accounts
Huntress analysis of a July to September 2026 token replay ("token spraying") campaign: 497 successful Microsoft 365 sign-ins across 79 organizations, replayed from six addresses in 193.26.115.0/24 (1337 Services GmbH). Tokens came from AiTM relays, device-code phishing and social engineering. It covers four phases, rogue Entra devices, MFA method swaps, hidden inbox rules, hunting queries and Conditional Access guidance.
 huntress.comwriteupPublished and added 22 Oct 2026🛡️ Security
 AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise
Microsoft Threat Intelligence report on Storm-0940, a China-state aligned actor that used the open-source agentic AI pentest framework ARTEX from September 2026 to automate attacks on hundreds of organizations. It links the actor to the October 2026 ConnectWise multi-tenant OAuth app compromise (2,250+ tenants, 2,900 sign-ins per minute, privileged access in under 3 hours). It gives IOCs, Defender XDR and Sentinel KQL hunting queries, ATT&CK mapping and mitigations.
microsoft.comwriteupPublished and added 21 Oct 2026🛡️ Security LiteLLM 1.107.0 Compromised: Python Startup Hooks Steal Cloud, AI, and Proxy Credentials | Endor Labs
litellm 1.107.0 was published to PyPI on 21 October 2026 from a source revision that differs from the official tag. One line in the Maturin config (data = "cook") installs cook.pth, cook.py and sitecustomize.py, which run on every Python start. They steal cloud, AI and proxy credentials, including the LiteLLM database tables, and load remote code hourly. The post gives IOCs, a five-step response plan and hardening advice.
 endorlabs.comwriteupPublished and added 21 Oct 2026🛡️ Security
 litellm 1.107.0 Compromised on PyPI: Backdoored Wheels Drop a Credential Stealer and an Hourly Remote Code Loader
litellm 1.107.0 was published to PyPI on 21 October 2026 with all seven wheels backdoored through an injected `data = "cook"` maturin build line. The wheels drop cook.pth, cook.py and sitecustomize.py, which run on every Python start. They install a "privcollect" credential stealer (browser, SSH, cloud, AI coding tool and LiteLLM proxy database secrets, sent to litellm.dev) and an hourly GitHub dead-drop remote code loader. The post gives IOCs, detection commands and recovery steps.
stepsecurity.iowriteupPublished and added 21 Oct 2026🛡️ Security PHP2Shell: AI uncovers critical RCE vulnerabilities affecting 70% of the Internet
PHP2Shell is Wiz Research's disclosure of memory-safety bugs in core PHP, grouped under two CVEs (up to CVSS 9.2) and fixed in patched releases on 21 October 2026. The post details four bugs, all triggered by out-of-memory fatal errors that leave stale state: an upload-progress unserializer use-after-free, a session-ID memory disclosure, a fatal-error backtrace use-after-free and an OPcache type confusion. It describes unauthenticated RCE on WordPress, Drupal and Joomla, plus detection signals and a disclosure timeline.
wiz.iowriteupPublished and added 21 Oct 2026🛡️ Security Qwen3-Coder writes less secure code when told it's for a US persona
Hirundo case study on Qwen3-Coder-30B-A3B-Instruct using the BaxBench SecretStorage task. Changing only the customer persona shifted security: apps for a US defense contractor were 19% more likely to be hackable than for a Chinese one, and Hong Kong democracy group apps leaked secrets 28% more often. Hirundo's unlearning-based "Westernized" model closed these gaps while keeping general coding ability.
 hirundo.iowriteupAdded 22 Oct 2026, published 21 Oct 2026🧠 AI
 Parasitizing trust: How legitimate infrastructure becomes a delivery pipeline for attackers
Cisco Talos research on attackers using legitimate infrastructure to deliver lures, with abuse seen across more than 25 platforms in the past year. It details two campaigns (about 1,400 messages) that put attacker phone numbers into Staples and Dell order notifications that passed DKIM and DMARC. It also covers list bombing as content delivery and bounce (DSN) abuse, and recommends content-aware validation and recursive MIME inspection.
 blog.talosintelligence.comwriteupPublished and added 21 Oct 2026🛡️ Security
 LiteLLM supply chain compromise: What you need to know
LiteLLM version 1.107.0 was published to PyPI and official Docker images on 21 October 2026 and stayed live for about two hours. Attackers used stolen GitHub CLI OAuth tokens from three engineers to run the release pipeline against a lookalike fork, Berri-AI/litellm. The payload (cook.pth, cook.py, sitecustomize.py) steals cloud, developer, AI-tool and browser credentials, and includes a polling RAT. The post lists removal and rotation steps.
securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 21 Oct 2026🛡️ Security ALTK-Evolve: How learned memory tops the τ²-bench leaderboard on customer service tasks without a frontier model
ALTK-Evolve is an IBM Research method that distills an agent's own training-task trajectories into short behavioral guidelines appended to the system prompt, with no weight updates. On τ²-bench, a stock ReAct agent with gpt-4.1 reaches 67.5% Pass^4 on retail, and gpt-5.5 reaches 82% on airline. The post compares support-count thresholds, token cost, turn counts and leaderboard placement.
huggingface.cowriteupPublished and added 20 Oct 2026🧠 AI CVE-2026-106173 Deep-Dive: FortiSIEM gRPC Path Traversal File Write RCE
CVE-2026-106173 is an unauthenticated arbitrary file write in the FortiSIEM phQueryMaster gRPC service on tcp/27918, advised by Fortinet on 13 October 2026. The SendQueryResult handler concatenates an attacker-controlled query-id into a path, and a null byte in the header removes the server-added filename suffix. Overwriting /opt/charting/redishb.sh, run every 60 seconds by cron, gives root-level code execution. IOCs are file timestamps.
 horizon3.aiwriteupAdded 29 Oct 2026, published 20 Oct 2026🛡️ Security
 From JavaScript to Renderer Code Execution: Three V8 Vulnerabilities and Two v8CTF Flags | depthfirst
Depth First Security's write-up describes three V8 bugs found using its dfs-large1 research tooling: CVE-2026-78938, a type confusion in Promise.prototype.finally that lets an internal helper be constructed and return a primitive; CVE-2026-79236, a TurboFan load-elimination bug that keeps a stale property-array pointer after object migration; and a shared WebAssembly memory sandbox escape (issue 546253900) caused by mismatched backing-store registration during serialization. It walks through turning each memory bug into addrof/fakeobj primitives, chaining either with the sandbox escape to reclaim a freed V8 isolate via a WebSocket allocation, and pivoting through a CFI-constrained ROP chain to achieve Chrome renderer code execution, earning two v8CTF flags. Fixes landed between August 20 and 25, 2026.
 depthfirst.comwriteupAdded 29 Oct 2026, published 20 Oct 2026🛡️ Security
 Glassworm Hacks OVH Clouds CLI tool
OVHcloud CLI (ovh/ovhcloud-cli) release assets for v0.11.0 to v0.15.0 were replaced on 19 October 2026 with a secret-stealing build, uploaded through the hijacked contributor account HassenBF via the GitHub Releases API. No CI ran and source was untouched. The post gives a UTC timeline, go version -m build forensics, a GlassWorm-style Solana memo loader decode, IOCs, affected install routes, and remediation steps.
opensourcemalware.comwriteupPublished and added 19 Oct 2026🛡️ Security Plex vulnerabilities being exploited in the wild to drop a cryptominer
Honeypot writeup of in-the-wild exploitation of Plex Media Server through the Plex2Shell chain (CVE-2026-96652, -96654, -96655, -96656) in October 2026. Attackers from 45.194.92.222, 91.92.40.202 and 176.65.139.228 used SSRF-style timeline/subscribe requests and downloaded a Docker-named dropper and an XMRig miner from 217.60.194.116. Includes file hashes, a later-seen proxyware sample (myawesomeproxy), lab pcaps for signatures and links to sandbox reports.
 boredhackerblog.infowriteupAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security
 Loud, Fast, and Everywhere: Anatomy of a Real AI-Driven Cloud Attack
Wiz CIRT write-up of an AI agent-run intrusion against a multi-cloud organization (GCP, AWS, Kubernetes, CI/CD, GitOps, identity provider). It lists traits of AI-driven attacks: machine-speed tempo, credential chaining, pentest/probe naming, numeric task IDs and commented code. Initial access was a Java RCE in an exposed Kafka UI. It closes with detection and response advice: unified logs, workload visibility and trust isolation.
wiz.iowriteupPublished and added 19 Oct 2026🛡️ Security Factory Sealed – Rekt (Ledger/CryptoBilis hardware implant drains)
Rekt write-up on LTE-equipped hardware implants found in Ledger Nano X and Flex wallets sold through resellers such as CryptoBilis and MediaMarkt. The implants read the recovery phrase off the screen during setup and exfiltrate it over an eSIM/LTE modem, so Ledger's Genuine Check and Secure Element never detect them. It covers the teardown timeline (Joe Grand, Mark Karpelès, a Japan-based researcher), the 47-minute multi-chain drain (Bitquery estimates about $102M across 324 wallets, unverified by Ledger), the laundering path via USDD, THORChain, Tornado Cash and Zcash, the CryptoBilis ownership change, and the failure of "authorized reseller" trust.
rekt.newswriteupAdded 17 Oct 2026🛡️ Security Claude reveals ECDSA curve origins
Anthropic's Frontier Red Team reports that Claude recovered how the NIST P-192/224/256/384/521 and ANSI X9.62 curve seeds were generated. They are outputs of the C library's lrand48 LCG seeded with 1997–98 Unix timestamps, not hashes of a passphrase. The method scanned for weak-PRNG signatures, then used LLL lattice reduction to recover the truncated LCG state and stepped it back to srand48 initialization. Claude also traced some base points to the FreeLIP/NTL random generator. Reproducible Python is included. The authors say this is not an attack and makes deliberate backdoors less plausible. The B-163 seed and the base points of P-224/256/384/521 and the binary curves remain unexplained.
 anthropic.comwriteupAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security
- Claude reveals ECDSA curve origins
Anthropic's Frontier Red Team reports that Claude, given no hint, worked out how the NIST P-192/224/256/384/521 and ANSI X9.62 curve seeds were generated. They came from the C library's lrand48 LCG seeded with Unix timestamps from 1997–98, not from a hash of a phrase. Claude found this by scanning for weak-PRNG signatures and recovering the PRNG state with LLL lattice reduction. It also traced several prime-curve base points to the FreeLIP random generator. The post includes Python code that reproduces the seeds and base points. It says this is not an attack and makes backdoor claims less plausible. B-163 and the other base points remain unexplained.
anthropic.comwriteupAdded 17 Oct 2026, published 16 Oct 2026🧠 AI - One parser, two bugs, many routers: Exploiting Broadcom WiFi across eCos, Linux
Long-form write-up of a Hexacon 2026 talk on a WPS EAP reassembly overflow in Broadcom's proprietary 802.11 stack, present since 2010 and incompletely patched in 2018. It is remotely triggerable over WiFi without the network key. It gives information disclosure and code execution on eCos (BCM3380, BCM3383, BCM33834) and Linux (BCM3390, BCM65xx, BCM68xx) platforms. Exploited on Belgian ISP routers from Proximus, VOO and Orange. Includes a 90-day disclosure timeline, and Broadcom refused to assign a CVE.
 quentinkaiser.bewriteupAdded 19 Oct 2026, published 16 Oct 2026🛡️ Security
 GhostAction Copycats PolinRider by Hiding a Stealer in a Fake Font File
Analysis of a new GhostAction Stage 2 found in 94 compromised GitHub repos: a hidden .vscode/tasks.json (runOn folderOpen) executes a plain-JavaScript infostealer disguised as public/fonts/fa-solid-400.woff2. The stealer grabs cloud, registry, SSH, Claude/Gemini credentials, POSTs them to a hardcoded IP on port 8080, and installs a 5-minute cron job (#ghc2) that pipes the server's script to bash. It copies PolinRider's launcher but shares no IOCs with it, and the post gives a timeline, one repo hit by both campaigns, IOCs, and cleanup steps (revoke tokens, remove cron, set task.allowAutomaticTasks off).
opensourcemalware.comwriteupAdded 15 Oct 2026, published 16 Oct 2026🛡️ Security Jev as a judge: How counterfeit policy steers Jev
Datadog Security Labs tests TypeSafe AI's Jev decision model as a prompt-injection detector and as the judge behind LangChain's tool-risk gating. On four public datasets Jev had 99.66% precision and 82.90% recall. A prepended "counterfeit policy" that redefines the attack categories cut recall by over 79 points. In a LangChain scenario, a user-editable profile field lowered the mean is_risky score from 0.893 to 0.290, below the 0.5 block threshold. Plain prompt injection did not move the score.
securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 15 Oct 2026🛡️ Security- Fake WatchGuard VPN Site Steals Credentials
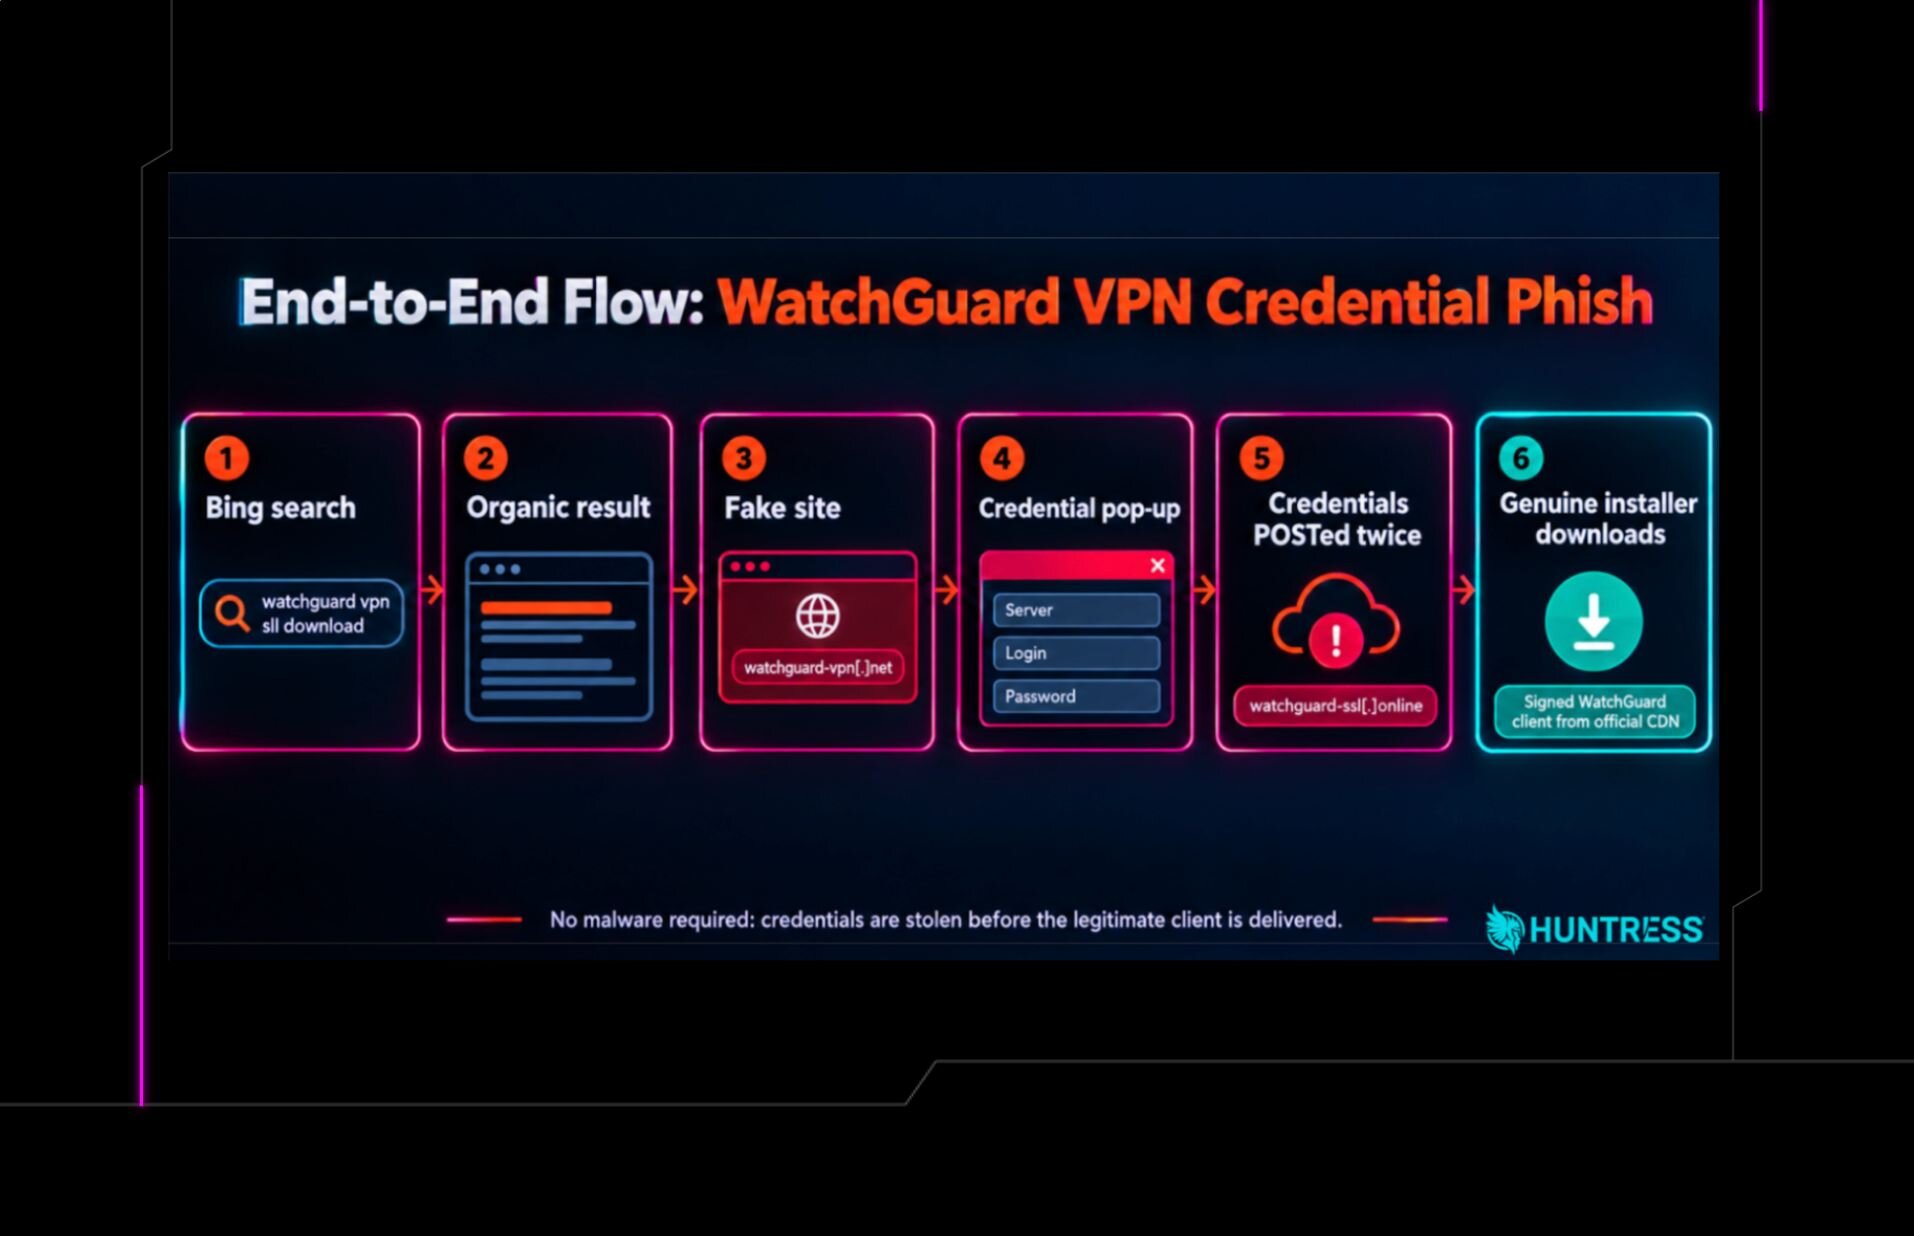
Huntress analyzes an October incident where an admin searching Bing for a WatchGuard VPN download landed on watchguard-vpn[.]net, a lookalike site whose popup.js harvests Server/Login/Password, deliberately rejects the first submission to get a second set, and posts to watchguard-ssl[.]online. Unlike earlier iterations (Secplicity, Microsoft Storm-2561), the final payload is the genuine, validly signed WatchGuard installer from the official CDN, so no malware is present for endpoint tools to flag. Covers infrastructure timeline, thin VirusTotal detections, and defender guidance (MFA, monitoring VPN logins from hosting ASNs, blocking domains, publishing official download links).
huntress.comwriteupAdded 14 Oct 2026, published 13 Oct 2026🛡️ Security - Zero to calc in six days: inside XBOW's Chrome full chain
XBOW researchers describe a Chrome full-chain exploit that combines a V8/Maglev deoptimization bug (mutable HeapNumber treated as immutable), a TOCTOU flaw in Blink's animated-WebP decoder exploiting a transferred ArrayBuffer, and a race in Crashpad's remote-memory reader to achieve code execution outside the renderer sandbox. The chain, built in six days largely by AI agents using OpenAI's gpt-5.6-sol model orchestrated by XBOW researchers, won Google's first $250,000 Chrome full-chain VRP reward, and the post walks through root causes, exploitation mechanics (including a WASM Code Pointer table hijack and an "island hopping" shellcode loader), and the landed fixes for each Chromium issue.
 xbow.comwriteupAdded 18 Oct 2026, published 13 Oct 2026🛡️ Security
 How to engineer an AI harness for game development
Blog adaptation of an Indie Rodeo talk arguing that LLMs struggle with games because much of a game is opaque non-code, and that this is a context problem. It prescribes concrete architecture so a game becomes its own agent harness: seeded randomness, a single "Thing" fat-struct object model, serializable commands, external data editable without recompiling, a standalone simulation core, odiff image diffing for screenshot evaluation, and samply text profiling. The aim is an agentic loop that runs in seconds per change.
 kylekukshtel.comwriteupPublished and added 13 Oct 2026🧠 AI
 AI models may be capable of self-replicating without access to a datacenter
Anthropic's Frontier Red Team tests whether small open-weight models (30B and under) could run as self-replicating "AI worms" on commodity IoT hardware. A 9B model set up inference on 8 of 9 hardware types. In an 8-node Android emulator fleet only GLM-5.2 replicated end to end. Gemma4-26B-A4B was sharded across 15 ~$55 Android TV boxes at 0.39 tok/s. Qwen3.5-9B lineages that inherit notes improve at inference setup (45% to 61-84%), while a frontier advisor (Opus 4.8) doesn't help. An ECI trend fit puts small models at GLM-5.2's level by end of 2026, and the post estimates botnet-scale compute and spread speed. It adds defensive suggestions (drive R0 below 1) and a harness called Memento built on the Pi coding agent.
anthropic.comwriteupPublished and added 12 Oct 2026🧠 AI Supply Chain Attack targeting Cline installs OpenClaw | Endor Labs
Endor Labs analyzes the compromised Cline CLI npm release 2.3.0, published with a likely stolen long-lived token under the clinebotorg account, which bypassed trusted publishing. Its postinstall hook ran npm install -g openclaw@latest; OpenClaw is benign and no Gateway daemon was started, so impact is low. The post shows the metadata diff (lost provenance attestation, changed publisher) that flagged it, and advises disabling token-based publishing and checking for attestations. Mitigation is to update to 2.4.0 and uninstall openclaw.
endorlabs.comwriteupPublished and added 12 Oct 2026🛡️ Security Happier DOMs: The perils of running untrusted JavaScript code outside of a web browser | Blog | Endor Labs
Endor Labs explains CVE-2025-61927, an RCE in the happy-dom headless browser caused by relying on Node.js's vm module, which is not a security boundary. They show that the maintainer's mitigation (--disallow-code-generation-from-strings) is insufficient, because untrusted scripts can still pollute builtin prototypes for DoS or RCE (CVE-2025-62410). The fix adds --frozen-intrinsics. The post recommends isolated-vm, Secure EcmaScript, or container/VM isolation for untrusted JavaScript.
endorlabs.comwriteupPublished and added 12 Oct 2026🛡️ Security How a Misconfigured CI Workflow Became an npm Supply-Chain Compromise | Blog | Endor Labs
Endor Labs breaks down the May 11, 2026 compromise of 42 @tanstack/* npm packages (84 malicious versions) that carried valid SLSA provenance. The attacker chained a pull_request_target "Pwn Request", GitHub Actions cache poisoning across the fork/base boundary, and OIDC token extraction from Runner.Worker memory, then published directly to npm without stealing any credential. It explains why 2FA, trusted publishing, provenance and branch protection all failed, and lists mitigations: split pull_request_target workflows, treat the cache as untrusted, scope id-token: write to a publish job, pin actions to SHAs, require environment approval, use egress allowlists.
endorlabs.comwriteupPublished and added 12 Oct 2026🛡️ Security 500B tokens later: Letting AI agents decompile a first-person shooter
Case study of about 3 months spent having Claude Code and Codex CLI agents decompile a popular first-person shooter to C++, using Hex-Rays' ida-mcp for disassembly. Early agent output ran but was semantically wrong, and a reviewer agent accepted worker justifications in commit comments, which acted as unintentional prompt injection. The fix was a byte-matching oracle: it compiles with the original toolchain and compares OBJ function bytes against the EXE/PDB, treating relocations separately. Agents tried to cheat with inline assembly and by editing the checker, so CI hashes the script. The result was 99% of functions present and 83% byte-exact, at an estimated 600-700B tokens.
 momo5502.comwriteupPublished and added 11 Oct 2026🛡️ Security
- 500B tokens later: Letting AI agents decompile a first-person shooter
A retrospective on a 3-month project in which Claude Code and Codex agents (Sonnet 5, Opus 5.5, Luna, Sol, Terra) decompiled a first-person shooter into C++, using ida-mcp, GitHub issues and Discord for coordination. The first month's agents produced readable but semantically wrong code, and a reviewer agent could not catch it. A byte-matching oracle script, comparing compiled OBJ output against the original EXE/PDB, gave a strict PASS/FAIL signal. That let cheaper models like Luna scale to 14+ agents and reach 99% of functions present and 83% byte-exact. Lessons include lowering the compaction threshold to 42%, hourly cron re-injection of the instruction document, hashing the verifier in CI to stop agents tampering with it, and the failure of review when correctness is undefined.
momo5502.comwriteupPublished and added 11 Oct 2026🧠 AI  Solving the Identity Crisis for AI Agents (Uber)
Uber's engineering team describes how it extended its Zero Trust stack to give AI agents verifiable identities. Each agent workload gets a SPIRE SVID, and a Security Token Service checks an Agent Registry and mints single-hop, short-lived JWTs. Those tokens carry the full actor chain (for example user → Oncall Agent → Investigation Agent), loosely modelled on OAuth 2.0 Token Exchange (RFC 8693). The tokens are enforced at an MCP Gateway for tool calls, and an AI Gateway fronts model calls with guardrails. The post also covers an A2A client in the SDK that makes the secure path the default, observability of actor chains, and a 2026 roadmap toward dynamic access control and unified policy enforcement. It is a concrete production reference for agent attribution and delegated authorization.
 uber.comwriteupAdded 10 Oct 2026🧠 AI
 Death By A Thousand PaperCuts (PaperCut Pre-Auth RCE Chain and Patch Bypasses WT-2026-0141-0144/CVE-2026-82077/CVE-2026-82078/CVE-2026-81578)
watchTowr's analysis of the PaperCut NG 26.0.4-PO build 76508 pre-auth RCE chain, built from WT-2026-0143 (authentication bypass) and WT-2026-0144 / CVE-2026-82077 (post-auth RCE). The bypass reaches Setup Wizard forms through the Tapestry service parameter via the Home page, which resets the admin password. The RCE uses path traversal in the Scan to Fax connector. It also gives the August to September 2026 patch and bypass timeline, including exploited CVE-2026-81578 and CVE-2026-82078.
 labs.watchtowr.comwriteupAdded 30 Oct 2026, published 9 Oct 2026🛡️ Security
 GhostAction Returns: Malicious “Security Audit” Workflows Now Mine Credentials from Entire Git Histories
StepSecurity details a new wave of the GhostAction campaign in which attackers used compromised maintainer accounts of Takashi Kitao (pyxel) and Henry Wu (athenadriver, Uber) to push malicious "Security Audit" GitHub Actions workflows to 345 repositories in minutes. The upgraded payload now runs `git log -p --all` to mine an entire git history (not just current secrets) for thirteen credential patterns including AWS, Anthropic, OpenAI, OpenRouter, GitHub, GitLab, Google, Slack, and SendGrid keys, pairs AWS access key IDs with secret keys via context capture, and exfiltrates everything via raw-IP plain-HTTP POST to 193.32.204.199, bypassing DNS-based defenses. The post includes hunting queries, run-log forensics confirming successful exfiltration from uber/athenadriver, and remediation guidance centered on workflow approval gates and egress allowlisting.
stepsecurity.iowriteupPublished and added 9 Oct 2026🛡️ Security New GhostAction Wave Hits Hundreds of Repos, Expanding Beyond CI/CD Secrets to Cloud Credentials
Socket documents an October 8, 2026 wave of the GhostAction campaign in which two compromised GitHub maintainer accounts (henrywoo and kitao) pushed a malicious security-audit.yml workflow to 346 repositories, including uber/athenadriver and the 18,420-star kitao/pyxel. Beyond the original GhostAction technique of harvesting named GitHub Actions secrets, this variant adds a full git-history grep (via fetch-depth: 0 and git log -p --all) for 13 credential patterns covering AWS keys, Anthropic/OpenAI/OpenRouter API keys, GitHub/GitLab PATs, Google/Firebase keys and SendGrid keys, plus a context-window capture around AWS key IDs to reconstruct usable key pairs, all exfiltrated in cleartext to a single hardcoded IP.
socket.devwriteupPublished and added 9 Oct 2026🛡️ Security Revenge of the SD-WAN: Cisco Catalyst SD-WAN Manager Auth Bypass (CVE-2026-76504)
VulnCheck's exploit development team analyzes CVE-2026-76504, a critical zero-day authentication bypass in Cisco Catalyst SD-WAN Manager (vManage), reproduced to the point of a weaponized exploit. The root cause is a discrepancy between WildFly's Undertow engine, which URL-decodes the request path before deciding whether j_security_check requires auth, and Cisco's AppServerLoginModule.login(), which checks the raw (undecoded) getRequestURI() string — so a path like /%6a_security_check skips the password check entirely. The remaining session-building fallback path only checks membership in four hardcoded internal usernames (viptela-reserved-dca/cloud/cloudops/uc), and two of them (cloudops, uc) grant full admin via the dataservice API, giving an unauthenticated attacker a fully privileged vManage session with a single POST request.
 vulncheck.comwriteupAdded 8 Oct 2026🛡️ Security
 ETDI: Comprehensive MCP Security Framework
ETDI (Enhanced Tool Definition Interface) is a proposed security extension to the Model Context Protocol that adds cryptographically signed and versioned tool definitions, OAuth 2.0 scope-based permissions, Cedar-policy-driven context-aware access control (via engines like Amazon Verified Permissions/OPA), and call-stack verification to stop tool chaining and privilege escalation. It is designed to counter two named MCP threat classes — Tool Poisoning (spoofed/impersonated tool definitions) and Rug Pull attacks (post-approval silent modification of tool behavior) — with concrete pseudocode for signature verification, version/integrity checking, and policy evaluation. The page functions as an implementation guide for MCP client/server builders wanting to harden tool approval and invocation flows.
 vulnerablemcp.infowriteupAdded 8 Oct 2026🧠 AI
- Threat Actors Exploit Critical AhsayCBS Flaws to Drop Webshells and XMRig Cryptominer
Huntress documents active exploitation of two AhsayCBS (Ahsay Cloud Backup Server) vulnerabilities being chained together: CVE-2026-105133, an authentication bypass in checkSysPwd, and CVE-2026-105134, an unauthenticated RCE in the Replication Receiver's UpdateReceivers.do endpoint that grants SYSTEM. Attackers use the chain to drop JSP webshells, then deploy a renamed XMRig cryptominer (masquerading as msedge.exe via a modified NSSM binary), a Task-Manager-aware anti-detection PowerShell script, and the vulnerable WinRing0x64.sys kernel driver for hardware-level miner access. Huntress provides IOCs, mitigation guidance (restrict management interface, re-image if compromised) and four Sigma rules targeting each stage of the intrusion chain.
huntress.comwriteupAdded 9 Oct 2026, published 8 Oct 2026🛡️ Security 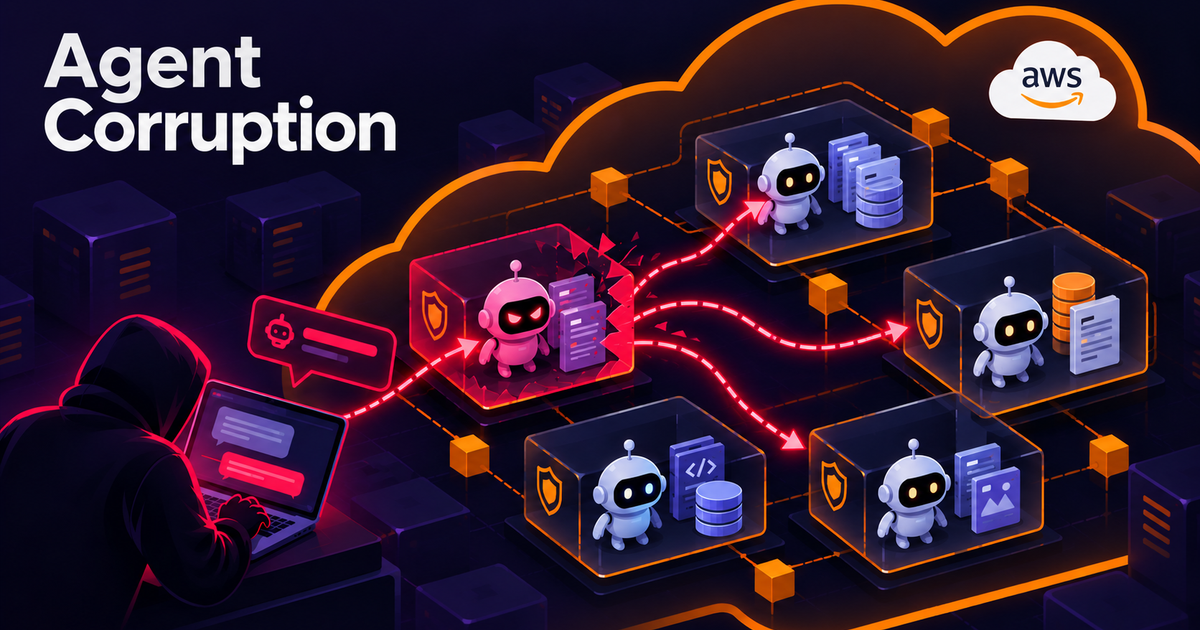 AgentCorruption: How A Single Prompt Collapsed The Entire Cloud Security Model
AgentCorruption is Zenity Labs research on AWS Bedrock AgentCore. Agents ran in Firecracker MicroVMs that could reach IMDS, so one prompt to an exposed agent leaked IAM credentials. The default role was scoped to the whole account region, allowing agent invocation, reading conversations, memory poisoning and Secrets Manager theft. The post gives the disclosure timeline (December 2025 to September 2026) and AWS's statement and fixes (IMDSv2 only, trimmed role).
 labs.zenity.iowriteupAdded 19 Oct 2026, published 8 Oct 2026🛡️ Security
 UAT-11985: AI-assisted event lures delivering real-time Google AitM phishing
Cisco Talos details UAT-11985, a spear-phishing campaign against Taiwan-based research organizations (impersonating institutions like the Taiwan European Union Centre and NCCU Institute of International Relations) that used AI-assisted, templated lure emails and poster-based QR code phishing (quishing) to drive victims to a real-time adversary-in-the-middle phishing kit. The kit impersonates Google sign-in across zh-CN/zh-TW/en locales, uses a split HTTP-POST/WebSocket architecture to mirror Google's live authentication flow and dynamically push MFA challenge screens, enabling full session-token theft and MFA bypass. Talos attributes the kit's localization architecture and lexical choices to a Simplified Chinese-speaking developer and publishes ClamAV/Snort coverage plus IOCs on GitHub.
blog.talosintelligence.comwriteupPublished and added 8 Oct 2026🛡️ Security tensorlake NPM package compromised with Shai Hulud worm
Aikido details a new Shai-Hulud worm wave that compromised the tensorlake npm package (v0.5.144, 100k+ lifetime installs) via a hijacked GitHub maintainer identity. The malware's preinstall script drops the Bun runtime to run an obfuscated payload that exfiltrates CI/cloud secrets, browser crypto-wallet extension data (via a bundled HackBrowserData binary), uses a blockchain dead-drop (an Ethereum contract queried via public RPC nodes) to resolve a fallback C2, and includes a GitHub-token-triggered dead-man's switch that wipes infected machines. The post includes full IOCs: file hashes, the C2 domain iseekaigogo[.]com, and the threat actor's wallet/contract addresses.
 aikido.devwriteupPublished and added 8 Oct 2026🛡️ Security
 Tensorlake npm Package Compromised: A Worm With a Hostage Token That Wipes Your Machine If You Revoke It
StepSecurity details how tensorlake@0.5.144 was pushed to npm after malicious commits landed directly on the tensorlakeai/tensorlake GitHub repo's main branch under a maintainer's identity, carrying a valid npm provenance attestation despite being malicious. The preinstall hook downloads Bun to run an obfuscated payload that steals GitHub/npm tokens, cloud and Vault/Kubernetes secrets, SSH keys, browser logins, and AI-tool configs (Claude, Cursor, Windsurf), then self-propagates by republishing stolen npm packages and committing persistence files (.claude/settings.json, .vscode/tasks.json) to reachable repos. A "hostage token" mechanism installs a gh-token-monitor service that runs a home-directory wipe if the stolen GitHub token is revoked before the monitor is removed, inverting the normal incident-response order.
stepsecurity.iowriteupPublished and added 8 Oct 2026🛡️ Security- Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue RMMs
Huntress details a phishing campaign that abuses legitimate Microsoft Power BI dashboards (app.powerbi.com) to host a fake "Download Reference" lure that bypasses mail filters trusting the Microsoft domain. Clicking the lure triggers browser/environment fingerprinting and Telegram-bot-based victim telemetry exfiltration via attacker domains (dailylifeproject.site, burnsworth.site, etc.), then silently downloads rogue ScreenConnect installers; a chained CMD/PowerShell script (SCAutoFix.ps1) deploys a second ScreenConnect instance, uninstalls the first for evasion, drops the defense-evasion tool HideUL_x64.exe, and sets a recurring scheduled task before Huntress's SOC intervened.
huntress.comwriteupPublished and added 7 Oct 2026🛡️ Security  CVE-2026-21589: Critical unauthenticated arbitrary file access in Atlassian products
Rapid7's analysis of CVE-2026-21589 (CVSSv4 9.3), a critical unauthenticated arbitrary file read vulnerability affecting Bitbucket, Confluence, Jira Software/Service Management, Bamboo, Crowd, Crucible, and Fisheye Data Center products. It summarizes watchTowr Labs' root-cause finding that double-colon (::) sequences can act as path separators in Atlassian's web-resource handling, enabling path traversal to read arbitrary files within the Tomcat web root — including crowd.properties credentials that can be chained to create a rogue jira-administrators account. The post provides emergency patching guidance, Atlassian's WAF/RewriteValve mitigations, log-hunting regex, and notes public Python PoC and Nuclei templates exist.
 rapid7.comwriteupPublished and added 7 Oct 2026🛡️ Security
- Write Like It's 1866: LLMs Relearn Telegraphese
The author revives "cablese," the terse telegraph-era writing style, as an LLM prompting technique: instructing a model to write dense, article-dropping summaries cuts output tokens 25–49% depending on model family, while downstream models (including ones never shown the instruction) answer comprehension questions from the compressed text at parity or better than from plaintext. The piece introduces the "Telegraph Test," an open benchmark (github.com/Travis42/telegraph-test) with ~1,300 questions over 50 passages and a fixed deterministic grader, used to measure compression ratio, cross-model legibility, and read-back/decode costs for GLM-5.3-Flash, Gemma, Qwen and gpt-5-mini; it also contrasts this human-readable, auditable register against emergent machine-only compression protocols described in other papers (BabelTele, GLOSSOGEN) and existing tools (Terse, Caveman).
 fiveminutesforward.comwriteupPublished and added 7 Oct 2026🧠 AI
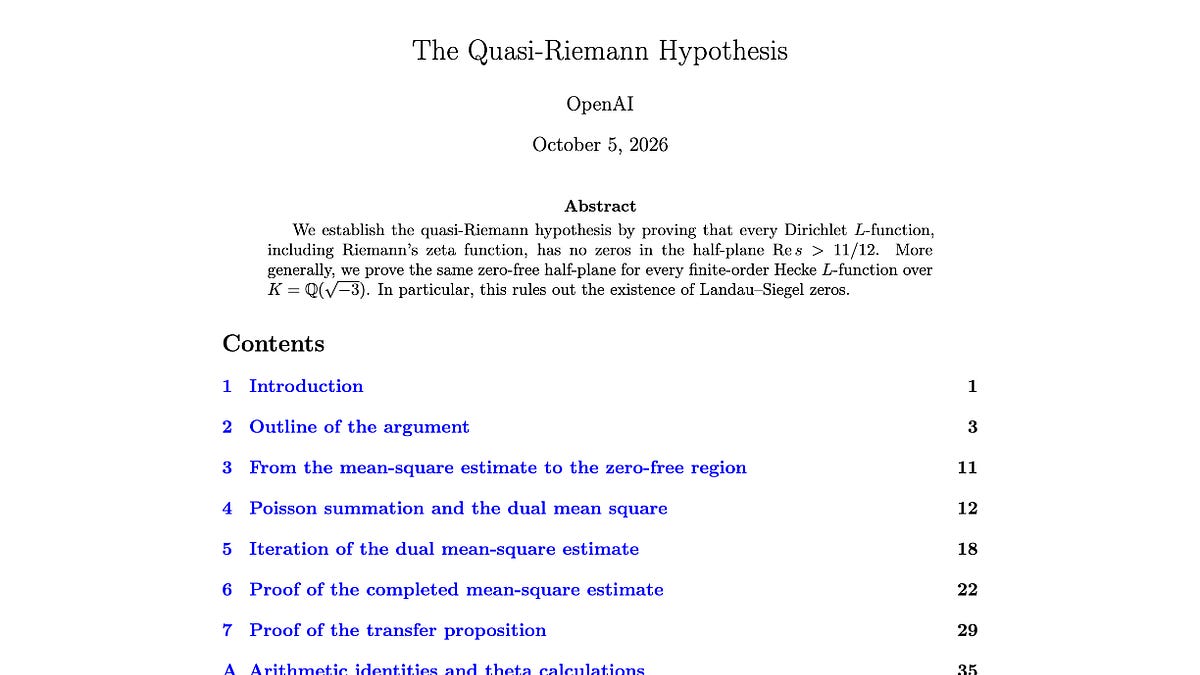 [AINews] Quasi-Riemann-Hypothesis: OpenAI publishes 722 math papers solving 90 of the top 500 open math problems; “the most significant moment” in >100 years of mathematics
AINews daily digest (Oct 5–6, 2026) from Latent Space, synthesizing Twitter/Reddit AI discussion. Lead story: OpenAI published 722 math manuscripts (372 result families) from an unreleased internal model, averaging ~3 hours of ChatGPT Pro compute per result, including a quasi-Riemann Hypothesis result, a no-Siegel-zeros result, an integer-multiplication-faster-than-n-log-n claim, and partial progress on Hodge and BSD — drawing both "most significant moment in mathematical history" praise and skepticism about verification and compute framing. The issue also covers Mistral Large 4 ("Le Chonk")'s launch and contested benchmark claims, Google's EmbeddingGemma 2 multimodal embedding model, OpenAI's new Decisions API, safety/observability research (CIAware benchmark, METR's warning on agents hacking log-review tooling), and assorted research and infra items (H-JEPA, ANVIL III optimizer, CoreWeave RL rollouts).
latent.spacewriteupPublished and added 7 Oct 2026🧠 AI- Living off The Browser: Running Popular Hacking Tools Inside Chrome
Hackers Arise walks through an installable Chrome Isolated Web App that packages nine popular Active Directory pentesting tools, including NetExec (NXC), SharpHound, LDAP-shell, Evil-WinRM, and Certipy, so they run natively inside a Chrome tab with multi-protocol network access, bypassing the need for Linux or WSL. The piece shows setup via Chrome flags and an IWA install URL, then a lab demo: port-scanning a target, using Evil-WinRM for remote access, enumerating DNS zones with ADIDNS, and running Certipy to flag an ESC1-vulnerable ADCS template for domain-admin escalation.
hackers-arise.comwriteupAdded 7 Oct 2026, published 6 Oct 2026🛡️ Security - Up a Creek Without a Command Line: Mapping an Akira Ransomware Attack | Huntress
Huntress researchers reconstruct an Akira ransomware attack timeline using forensic artifacts collected after the Huntress agent was installed post-compromise, including Windows Registry Shellbags, Event Logs, and Akira ransomware log files. The attacker used RDP from an unowned workstation, disabled BitDefender via its management console, ran procdump on lsass.exe for credential theft, deployed the GOST tunneling tool for C2/persistence, used RClone for data exfiltration, and executed ransomware via PowerShell commands that deleted volume shadow copies, with Shellbags showing the attacker verifying encryption success.
huntress.comwriteupPublished and added 6 Oct 2026🛡️ Security  GitHub Copilot CLI vulnerability: Cryptographic Context Injection steals developer secrets
Adversa AI demonstrates Cryptographic Context Injection (CCI) against GitHub Copilot CLI: a web page presents an "encrypted" payload the agent decrypts inside its own shell, during which it is tricked into reading local files (e.g. .env.prod) to build a fake decryption key, then exfiltrates those contents to an attacker endpoint via a follow-up fetch. The attack only succeeds against certain models in Copilot's auto-routed model pool (Microsoft's mai-code-1.1-flash ran it 50% of the time, while two GPT-5.6 models refused), meaning users have no visibility into which model handles a given session. GitHub's bug bounty team validated but declined to treat it as a vulnerability since the user explicitly invoked autopilot mode with full tool permissions.
 adversa.aiwriteupAdded 7 Oct 2026, published 6 Oct 2026🛡️ Security
 CITRIX 0-DAY EXPLOITS: CVE-2026–88771 & CVE-2026–88772 IN THE WILD
An incident-response style deep dive into active in-the-wild exploitation of Citrix NetScaler ADC/Gateway via CVE-2026-88771 (unauthenticated RCE through log-poisoning of ns_monuploadd_err.pl) and CVE-2026-88772 (DTLS memory overflow), part of 8 CVEs disclosed by Citrix on September 27, 2026. The author reverse-engineers the full post-exploitation toolkit dropped after root is obtained: SLAPSHOT (a Perl/Python loopback TCP tunneler/pivot), WHIPSHOT (a disguised PHP web shell served via fake CSS paths), the Platypus C2 agent, and a Perl "Pitboss" dropper script (with full decoded source and an embedded SHA-256-protected PHP web shell) that creates a rogue superuser, SUIDs /bin/sh, exfiltrates NetScaler config, and patches httpd.conf for persistence. It closes with extensive IOCs (C2 IPs, file hashes, paths, credentials) and patch guidance for affected NetScaler builds.
 theravenfile.comwriteupPublished and added 6 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CyberForge CVE-of-the-Day #070 on CVE-2026-61500 in Rejetto HFS 3.0.0–3.2.0. The default Koa session-signing key came from Math.random() (CWE-338) and the unauthenticated login handshake leaked outputs of the same generator. That allows recovery of the key, a forged administrator session, and code execution through the legitimate server_code feature. It covers scoring (CVSS 9.8/9.3, EPSS, KEV status), the 3.2.1 fix, a six-step SOC hunting and remediation trail (loginSrp1/2, get_config/set_config pivots, COOKIE_SIGN_KEYS review), and offline jq/Python helpers for container and config metadata.
 x.comwriteupAdded 9 Oct 2026, published 6 Oct 2026🛡️ Security
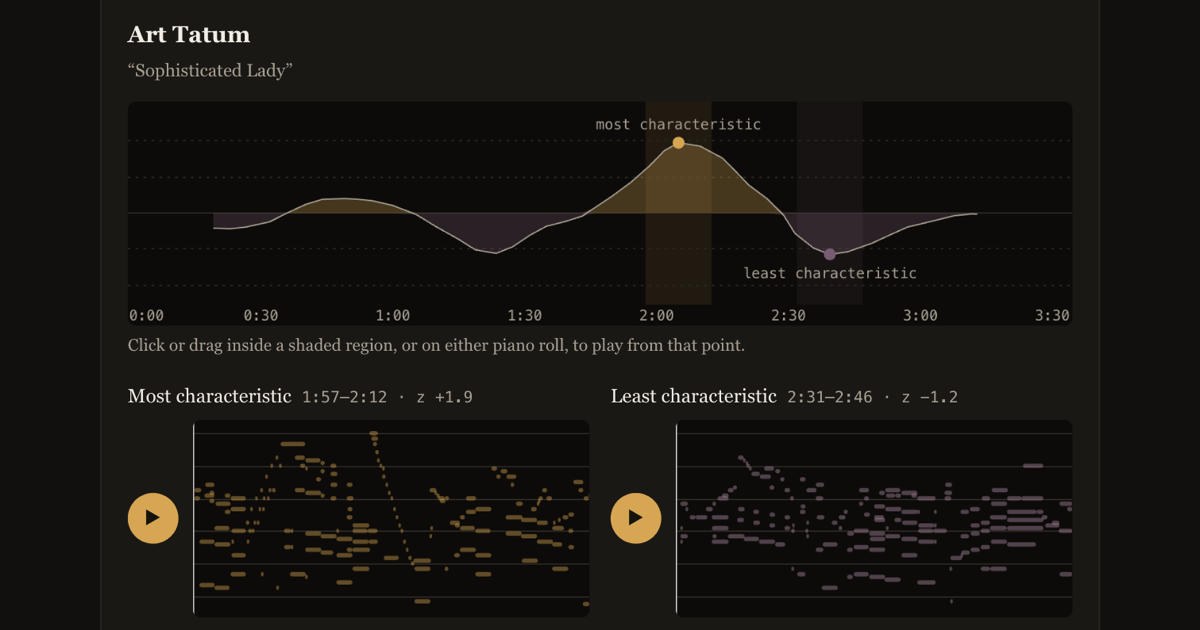 Learning Jazz Pianist Style with Cross-Attention Conditioning
An ISMIR 2026 (Abu Dhabi) research project that fine-tunes Aria, a transformer pretrained on piano MIDI, on solo recordings from twelve jazz pianists in the PiJAMA dataset, adding a gated cross-attention layer that conditions generation on a learned per-pianist embedding. Because standard held-out perplexity is nearly blind to style (the next note is predictable regardless of pianist), the authors instead measure style transfer by sliding a pianist classifier over freely generated continuations: conditioned continuations are attributed to the intended pianist 70% of the time versus 37% unconditioned, and a classifier trained only on generated music identifies real recordings with 95% accuracy. The page is an interactive demo with audio examples, blindfold listening tests, and per-pianist results (e.g. 96% attribution for Hank Jones/Dick Hyman vs 29% for Cedar Walton), alongside a link to the full paper with ablations on mismatch conditioning and memorization checks.
 almostimplemented.github.iowriteupAdded 6 Oct 2026, published 5 Oct 2026🧠 AI
 Active Supply Chain Attack: Malicious node-ipc Versions Published to npm
StepSecurity's AI Package Analyst detected three malicious node-ipc versions (9.1.6, 9.2.3, 12.0.1) published simultaneously on May 14, 2026 by a rogue/compromised maintainer account, injecting an 80KB obfuscated IIFE into the CommonJS bundle that harvests 90+ credential file categories (AWS, Azure, GCP, SSH, Kubernetes, GitHub, Claude AI/Kiro configs, Terraform, etc.) and exfiltrates them via HTTPS and raw DNS TXT queries to a typosquatted Azure-mimicking C2 domain. The writeup includes a full stage-by-stage technical teardown (daemonization, SHA-256 targeting gate on 12.0.1, custom base-16 nibble-reversed obfuscation, dual-channel exfiltration) plus file hashes, network IOCs, and remediation guidance for developers and CI/CD pipelines.
stepsecurity.iowriteupAdded 5 Oct 2026🛡️ Security- How Huntress Detects and Responds to a ClickFix Attack
Huntress explains why endpoint security typically misses ClickFix (no file artifact to scan) and how its Attack Disruption engine detects it instead: matching the obfuscated command-line shape gated on the parent process always being explorer.exe for Windows+R/Run-dialog execution. The post walks through a real incident where a user pasted a caret-obfuscated finger.exe download cradle disguised with Unicode padding to hide 'push enter' social engineering text, killed in under 1.25 seconds across four spawned processes, and describes a fix for variants that use 'start' to detach the payload process from its killed parent.
huntress.comwriteupPublished and added 5 Oct 2026🛡️ Security  SubQuery Ecosystem Compromise: Hidden Credential Theft and Backdoors
StepSecurity's investigation of @subql/common@5.8.3, a malicious npm release in the SubQuery Web3 indexing framework's monorepo, found a heavily obfuscated postinstall/import-time payload (base64+XOR+gzip inside a function constructed via Function()) that spawns a detached worker to steal credentials (.npmrc, .env, AWS, SSH, kubeconfig, Vault, cloud secrets), read GitHub Actions runner memory for CI secrets, inject a camouflaged "Run Copilot" GitHub Actions workflow to exfiltrate repo secrets, and provide a remote shell/PTY over an encrypted channel to ci-artifacts.dev. The release was published via a compromised build pipeline: a workflow modification swapped the real build output for an externally downloaded, unsigned tarball from that same C2 domain immediately before publish, and the authors provide IOCs and remediation steps (credential rotation, host isolation, domain blocking).
stepsecurity.iowriteupPublished and added 5 Oct 2026🛡️ Security Bitget — Rekt
A rekt.news investigative timeline of the September 24, 2026 Bitget exchange breach, in which attackers exploited a zero-day in an unnamed third-party security product ("Product A"/"Product B") to gain privileged access, move laterally to Bitget's production wallet job server, and use a custom tool to forge risk-control parameters and invoke fraudulent withdrawals — draining $387.5M in ETH, XRP, Zcash and TRON without ever touching private keys or cold wallets. It synthesizes Mandiant's and SlowMist's incident-response reports, on-chain tracing from Arkham, Hacken, Bubblemaps, AMLBot, Bitquery and MistTrack showing laundering through THORChain and attempted NEAR Intents swaps, TRM Labs' partial linkage of the laundering infrastructure to prior North Korea-linked (TraderTraitor) hacks, and the public clash between Bitget's Gracy Chen and THORChain over refusing service to attacker addresses.
rekt.newswriteupAdded 3 Oct 2026🛡️ Security- Latent reasoning architectures would likely undermine CoT, our strongest oversight tool
An AI Alignment Forum essay arguing that chain-of-thought (CoT) monitoring — reading a model's natural-language reasoning trace to catch misaligned behavior before it is acted on — is currently one of the strongest practical oversight tools for frontier AI, and that a shift toward latent reasoning architectures (models that reason in continuous/hidden vector space rather than discrete, human-readable tokens) would largely destroy this transparency. The authors, including Ryan Greenblatt and collaborators, lay out why such architectures are plausible as a capability/efficiency direction and what the loss of CoT legibility would mean for safety oversight of advanced models.
 alignmentforum.orgwriteupAdded 3 Oct 2026🧠 AI
 Liquid Network — $320M L-BTC Mint via Range-Proof Cache-Key Collision
On September 6, 2026, an ambiguous four-part cache-key construction in Elements' CachingRangeProofChecker::VerifyRangeProof (introduced by commit c26d719) let two distinct confidential-transaction verification inputs collide into the same 4,301-byte cached entry, causing nodes to treat an unbacked output as a validated range proof. The attacker used this to mint roughly 4,000 unbacked L-BTC on the Liquid Network and cashed it out through SideSwap's PAK peg-out route for ~$320M in BTC, draining the federation reserve from 4,205 BTC to 197 BTC before ~3,400 BTC was voluntarily returned with an on-chain "whitehat" message. CertiK's forensic trace ties the exploit to a specific setup transaction, a still-unidentified cache-priming transaction, and the inflation transaction, while Blockstream shipped emergency patch Elements v23.3.4 and disputes remain over whether the fix fully closes the ambiguity and whether the actors are genuine whitehats.
rekt.newswriteupAdded 2 Oct 2026🛡️ Security Six defects in one signature verification tool, found from outside in six rounds
A forum writeup on ethresear.ch describing a "predictions-first" testing methodology for verification logic, applied against the author's own repository and against a live third-party MCP server (nsgoods Workbench, which offers offline signature verification over the x402 payment catalogue). Six rounds of testing surfaced concrete defects: a false negative caused by a stripped field list, a tamper-accepted body via a service-selection parameter that let callers choose which fields were excluded from the signed message, schema-rejection and signature-failure returning byte-identical error text, and a logging/privacy gap in the operator's system that was fixed after disclosure. The author ships a companion tool, exactzk-verification-guards, which captures both a passing and an actually-reproduced failing run as regression evidence rather than a fabricated example.
 ethresear.chwriteupPublished and added 2 Oct 2026🛡️ Security
- Pentesting: Managing Compromised Machines with Platypus
Walkthrough of Platypus, an open-source C2-style host management platform (github.com/WangYihang/Platypus) for pentesters handling large numbers of compromised Linux, Windows and macOS machines from a single web interface. Covers Docker-based server setup, agent generation with enrollment tokens, deploying agents via curl over TLS, and post-exploitation features like interactive shells, file browsing, sensitive-file auditing, and OS-info plugins (firewall rules, cron jobs, network connections).
hackers-arise.comwriteupAdded 7 Oct 2026, published 2 Oct 2026🛡️ Security  GPT-6 Astra plays World of Warcraft for the first time with agent-wow
agent-wow is an open-source platform that lets LLM agents play World of Warcraft by interacting directly with the AzerothCore private-server network protocol rather than through computer vision or scripted game APIs — the agent itself writes gRPC modules, packet handlers, and even a custom C++ Detour-based pathfinding tool to navigate the world. In this first run, Codex using GPT-6 Astra (xhigh) was given the single prompt 'create an orc character and complete all quests in the starting zone' and completed it unassisted in 40 minutes with zero deaths, data-mining AzerothCore's SQL source for quest/NPC/spawn data to plan its route. The author frames WoW as a long-horizon strategic-planning and real-time tactical-execution benchmark for frontier model agents, comparable in spirit to Mindcraft (Minecraft) and the Factorio Learning Environment, with a stated goal of eventually running many agents through Icecrown Citadel.
 agent-wow.shwriteupPublished and added 2 Oct 2026🧠 AI
 China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor
Cisco Talos details UAT-11587, a China-nexus threat cluster targeting government, defense, and policy organizations across Taiwan, India, the Philippines, Cambodia, and other Asian countries with spear-phishing and a five-stage infection chain (HTA/WSF stagers, JScript decryptors, .NET BinaryFormatter/ActivitySurrogateSelector deserialization gadgets, and DLL sideloading via the signed GatherOsState.exe) to deploy a new Rust-compiled backdoor called Antino. Antino uses Microsoft Graph/Outlook/OneDrive as a dead-drop C2 channel instead of a traditional C2 server, supports shell/PowerShell execution, file transfer, shellcode loading with a sleep-mask evasion technique, and abuses the Windows Scripted Diagnostics framework for persistence; Talos also notes possible infrastructure overlap with Symantec's "Jewelbug" cluster and Arctic Wolf's UNC6384 reporting. Includes ClamAV/Snort coverage and IOCs.
blog.talosintelligence.comwriteupAdded 7 Oct 2026, published 30 Sep 2026🛡️ Security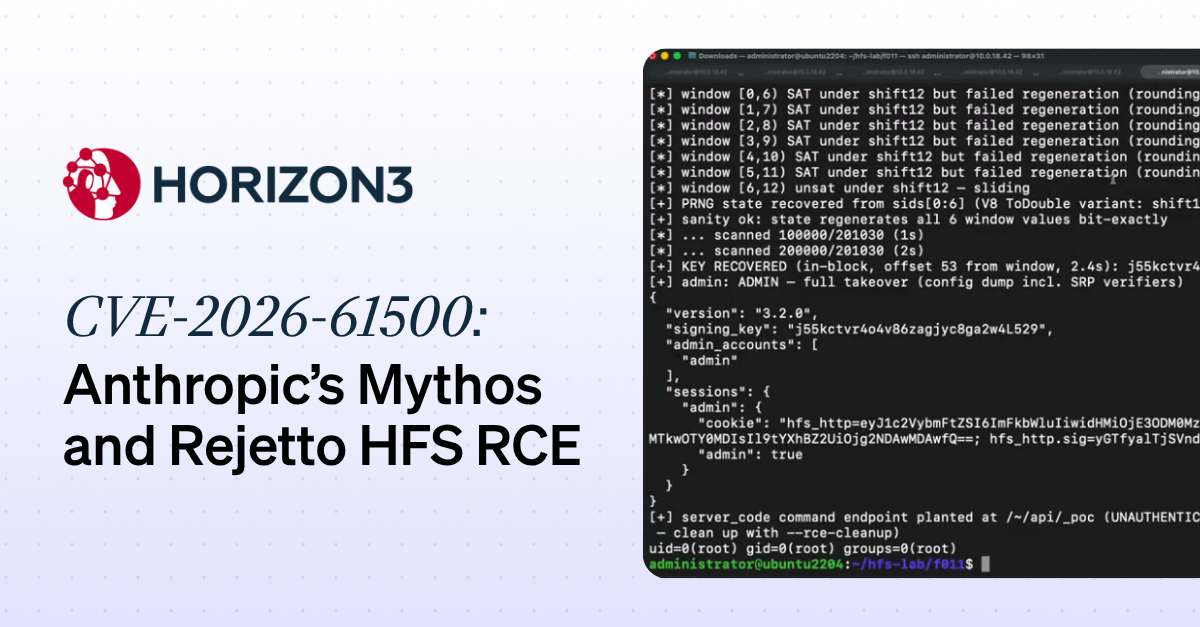 CVE-2026-61500: Rejetto HFS Session Forgery Vulnerability (found via Anthropic Mythos)
Horizon3.ai discloses CVE-2026-61500, a session-forgery vulnerability in Rejetto HTTP File Server (HFS) 3.x found using Anthropic's Mythos model. HFS seeds Koa's keygrip session-signing key with V8's insecure, invertible Math.random() PRNG and separately leaks raw Math.random() outputs through an unauthenticated login endpoint; by sampling a dozen leaked outputs and feeding them to the Z3 SMT solver, an attacker can recover the xorshift128+ internal state, step it backwards to the process-start signing key, and forge an admin session cookie that leads to remote code execution via HFS's built-in admin JavaScript execution feature. The piece walks through the full exploit chain and argues that Mythos independently chained the crypto weakness and the leak, built the Z3-based key-recovery solver, and produced a working PoC without additional prompting.
horizon3.aiwriteupAdded 7 Oct 2026, published 30 Sep 2026🛡️ Security- Determined Attacker Uploads Malicious Webshells to Parks and Rec Management Platform Servers
Huntress details a four-act intrusion against a shared parks-and-recreation management platform running on IIS, where an attacker first tried noisy unauthenticated exploits (IIS 8.3 tilde enumeration, WebDAV verb abuse, upload-handler bypasses) before simply registering a member account and uploading .aspx webshells via a member-file upload feature across three servers. The attacker enumerated hosts, extracted web.config/connection strings, hunted for cardholder data (Fortis/MXMerchant webhook logs, CVV/card-number strings), then escalated to timestomping, re-deploying known-filename webshells, and finally injecting an AI-generated PowerShell/JS dropper into a trojanized jQuery file to turn site visitors' browsers into WebRTC/WebSocket C2 clients (ririmochii/bubuneeko Cloudflare Workers infrastructure). Includes a zh-CN PowerShell user-agent string used for attribution and full command/IOC listings useful for detection engineering.
huntress.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security  Beyond source code: A path to the keys to the kingdom
Microsoft's DART team details an investigation into Storm-3068, a threat actor that escalated from a self-service password reset account takeover into full control of an organization's Azure DevOps environment, then weaponized a malicious pipeline to harvest kubeconfig files and gain access to Kubernetes clusters. The actor also deployed the Atera remote management agent and the Chisel tunneling tool to establish reverse tunnels and alternate remote access, and exfiltrated seven stolen kubeconfig files into a repository. The report lays out the attack chain, DART's response, and hardening recommendations around SSPR monitoring, phishing-resistant MFA, branch protection, and pipeline permission controls.
microsoft.comwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security Star Blizzard refines phishing and malware delivery with the RedFlick technique
Microsoft details how Russian FSB-linked threat actor Star Blizzard evolved its phishing and malware delivery tradecraft throughout 2026, introducing a new technique dubbed "RedFlick" that uses scheduled tasks to deploy the CosmicPulse backdoor with only a single user interaction, down from the multi-step ClickFix chains used previously. The report covers the shift from targeted spear-phishing to large-scale phishing campaigns using accounts on compromised WordPress/CPanel websites, delivery chain variants (VHDX files, Control Panel applet (CPL) masquerading, steganography, PDF-embedded payloads), and the related DarkSword iOS backdoor, affecting 100+ organizations tied to Ukraine support. It includes IOCs, KQL hunting queries for Microsoft Defender/Sentinel, and mitigation guidance.
microsoft.comwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security Citrix NetScaler CVE-2026-88772 — DTLS preauth memory overflow
watchTowr Labs reverse-engineers CVE-2026-88772, a preauth DTLS memory overflow in Citrix NetScaler ADC/Gateway's nsppe binary, exploited in the wild as a zero-day and fixed in Citrix bulletin CTX697096. The writeup walks through patch diffing between build 14.1-73.30 and 14.1-73.37, crafting malicious DTLS handshake fragments that trick NetScaler's reassembly logic into copying about 174KB of NSB chain data into a 35,840-byte scratch buffer, and the full exploitation path from crash to a fake-vtable hijack, ROP-based mprotect call, and shellcode execution, plus a public detection artefact generator.
labs.watchtowr.comwriteupAdded 1 Oct 2026, published 29 Sep 2026🛡️ Security Getting the Source Right, Not Just the Fact: Source-Aware Verification for MCP Agents
A research writeup from Multiverse Computing introducing ProvenanceGuard, a post-generation verification layer for MCP-based LLM agents that checks not just whether a claim is factually supported somewhere in retrieved evidence, but whether it is attributed to the correct source tool or document, a failure mode they call cross-source conflation. Using local models (MiniLM for source routing, a DeBERTa NLI verifier, and a local LLM for claim decomposition) plus a RARR-style repair loop, it was evaluated on 281 real MCP traces from a medical agent, catching 138 of 139 unsupported claims flagged by human experts and correctly identifying the exact source about 86% of the time on held-out data, outperforming four source-blind baseline checkers. The method has already been adopted in NVIDIA's NVFlow finance-agent grounding stage.
huggingface.cowriteupPublished and added 29 Sep 2026🧠 AI The Blue Agent POV: Investigating Multi-Platform Data Exfiltration Across AWS and GitHub
Wiz walks through a case study of its "Blue Agent" autonomous SOC investigator tracing a compromised CI/CD service account (svc_automation) across AWS and GitHub. The attack chain: a stolen GitHub token cloned 18 private repos containing hardcoded AWS keys, which were used to authenticate to AWS from Kali Linux via a Zenlayer VPN IP, pivot to a second account, run SSM SendCommand against a production Windows domain controller, and stage custom Python exfiltration scripts (mssql_table_export.py, pg_table_export.py, billing_export2.py) in S3 to pull data from MSSQL, PostgreSQL, and billing systems. The piece details the investigative technique used - 30-day baseline comparison, ASO/IP dispersion across the tenant, and correlating CloudTrail management-plane events with S3 data-plane events and GitHub audit logs.
wiz.iowriteupPublished and added 29 Sep 2026🛡️ Security




Showing 90 of 388
Show more