- Field Notes: Reconstructing an Attacker’s Workflow
Field note from dfir.ch on PowerShell scripts an attacker left on disk during an incident: a file-watching command runner using Invoke-Expression, a fake Windows credential prompt that validates passwords via Start-Process and logs them in cleartext, AD computer enumeration with WMI access testing, and SMB share discovery via NetShareEnum. It notes where script labels overstate what they prove and lists hunting strings for Event IDs 4104, 4103, 4688 and Sysmon 1.
 dfir.chwriteupAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security
- Field Notes: EtherRAT Distributed Through a Legitimate Intune Workflow
DFIR case where a malicious MSI impersonating Advanced IP Scanner, sourced from a fake GitHub repo found via Bing, was imported by a customer into Microsoft Intune and deployed to four endpoints, running a Node.js-based EtherRAT chain. It traces the infections by correlating the MSI ProductCode, MDMAppInstaller/omadmclient process ancestry and Intune app inventory (Graph PowerShell query). It also covers renamed node.exe hash-hunting pitfalls, Ethereum RPC dead-drop C2 traffic, a screen-capture script and a second impersonating repo.
dfir.chwriteupAdded 14 Oct 2026, published 13 Oct 2026🛡️ Security - Threat Actors Exploit Critical AhsayCBS Flaws to Drop Webshells and XMRig Cryptominer
Huntress documents active exploitation of two AhsayCBS (Ahsay Cloud Backup Server) vulnerabilities being chained together: CVE-2026-105133, an authentication bypass in checkSysPwd, and CVE-2026-105134, an unauthenticated RCE in the Replication Receiver's UpdateReceivers.do endpoint that grants SYSTEM. Attackers use the chain to drop JSP webshells, then deploy a renamed XMRig cryptominer (masquerading as msedge.exe via a modified NSSM binary), a Task-Manager-aware anti-detection PowerShell script, and the vulnerable WinRing0x64.sys kernel driver for hardware-level miner access. Huntress provides IOCs, mitigation guidance (restrict management interface, re-image if compromised) and four Sigma rules targeting each stage of the intrusion chain.
 huntress.comwriteupAdded 9 Oct 2026, published 8 Oct 2026🛡️ Security
- Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue RMMs
Huntress details a phishing campaign that abuses legitimate Microsoft Power BI dashboards (app.powerbi.com) to host a fake "Download Reference" lure that bypasses mail filters trusting the Microsoft domain. Clicking the lure triggers browser/environment fingerprinting and Telegram-bot-based victim telemetry exfiltration via attacker domains (dailylifeproject.site, burnsworth.site, etc.), then silently downloads rogue ScreenConnect installers; a chained CMD/PowerShell script (SCAutoFix.ps1) deploys a second ScreenConnect instance, uninstalls the first for evasion, drops the defense-evasion tool HideUL_x64.exe, and sets a recurring scheduled task before Huntress's SOC intervened.
huntress.comwriteupPublished and added 7 Oct 2026🛡️ Security - Up a Creek Without a Command Line: Mapping an Akira Ransomware Attack | Huntress
Huntress researchers reconstruct an Akira ransomware attack timeline using forensic artifacts collected after the Huntress agent was installed post-compromise, including Windows Registry Shellbags, Event Logs, and Akira ransomware log files. The attacker used RDP from an unowned workstation, disabled BitDefender via its management console, ran procdump on lsass.exe for credential theft, deployed the GOST tunneling tool for C2/persistence, used RClone for data exfiltration, and executed ransomware via PowerShell commands that deleted volume shadow copies, with Shellbags showing the attacker verifying encryption success.
huntress.comwriteupPublished and added 6 Oct 2026🛡️ Security - The First 24 Hours: What Happens When Ransomware Lands
An hour-by-hour ransomware incident response playbook written by UnderDefense CEO Nazar Tymoshyk and published on Huntress's blog, covering confirmation, containment, exfiltration detection, backup/recovery pitfalls, and root-cause investigation in the first 24 hours of an attack. It draws on Mandiant's M-Trends 2026 report (14-day median dwell time, 22-second access-broker-to-ransomware handoff) and CISA's November 2025 Akira advisory (VPN without MFA as primary access vector, exfiltration via FileZilla, WinRAR, WinSCP, RClone, Mega and Ngrok, credential dumping with Mimikatz and LaZagne, PowerShell-based shadow copy deletion) alongside real UnderDefense engagement anecdotes.
huntress.comwriteupAdded 3 Oct 2026, published 2 Oct 2026🛡️ Security - Defender Exclusion Abuse: How Attackers Hide Malware from MDAV
Huntress breaks down how Microsoft Defender Antivirus (MDAV) path/extension exclusions can be abused to hide malicious binaries from scans, detailing the registry internals (HKLM...Windows Defender\Exclusions vs the GPO-driven Policies key) and the four ways to set them: PowerShell (Set/Add-MpPreference), the MSFT_MpPreference WMI class, GPO, and direct registry edits. It documents real-world abuse by GootKit (2019), WhisperGate (2022), and Muddled Libra (2024), plus an under-documented trick where setting HideExclusionsFromLocalAdmins blocks even SYSTEM from querying exclusions via PowerShell/WMI, and describes the registry-level telemetry and detections Huntress built to catch both behaviors.
huntress.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security  China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor
Cisco Talos details UAT-11587, a China-nexus threat cluster targeting government, defense, and policy organizations across Taiwan, India, the Philippines, Cambodia, and other Asian countries with spear-phishing and a five-stage infection chain (HTA/WSF stagers, JScript decryptors, .NET BinaryFormatter/ActivitySurrogateSelector deserialization gadgets, and DLL sideloading via the signed GatherOsState.exe) to deploy a new Rust-compiled backdoor called Antino. Antino uses Microsoft Graph/Outlook/OneDrive as a dead-drop C2 channel instead of a traditional C2 server, supports shell/PowerShell execution, file transfer, shellcode loading with a sleep-mask evasion technique, and abuses the Windows Scripted Diagnostics framework for persistence; Talos also notes possible infrastructure overlap with Symantec's "Jewelbug" cluster and Arctic Wolf's UNC6384 reporting. Includes ClamAV/Snort coverage and IOCs.
 blog.talosintelligence.comwriteupAdded 7 Oct 2026, published 30 Sep 2026🛡️ Security
- Determined Attacker Uploads Malicious Webshells to Parks and Rec Management Platform Servers
Huntress details a four-act intrusion against a shared parks-and-recreation management platform running on IIS, where an attacker first tried noisy unauthenticated exploits (IIS 8.3 tilde enumeration, WebDAV verb abuse, upload-handler bypasses) before simply registering a member account and uploading .aspx webshells via a member-file upload feature across three servers. The attacker enumerated hosts, extracted web.config/connection strings, hunted for cardholder data (Fortis/MXMerchant webhook logs, CVV/card-number strings), then escalated to timestomping, re-deploying known-filename webshells, and finally injecting an AI-generated PowerShell/JS dropper into a trojanized jQuery file to turn site visitors' browsers into WebRTC/WebSocket C2 clients (ririmochii/bubuneeko Cloudflare Workers infrastructure). Includes a zh-CN PowerShell user-agent string used for attribution and full command/IOC listings useful for detection engineering.
huntress.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security  Phishing Abuses RMM Tools for Persistent Access
Microsoft Defender Experts document a July 2026 phishing campaign that delivers a masqueraded but legitimately signed MSP360 RMM installer (v2.5.0.67) via meeting-invite, Zoom, Adobe, and DHL-themed lures hosted on both attacker infrastructure and legitimate cloud services (S3, Cloudflare R2, Dropbox, GitLab, Supabase). After UAC-elevated installation and service persistence, the RMM.Agent.exe service launches PowerShell to silently install a ConnectWise ScreenConnect client via msiexec, which the actor then uses via RunFile to drop credential-theft and reconnaissance tools disguised as Windows/Defender/Phone Link components. A separate July intrusion used FaronicsDeployAgent.exe the same way to deploy ScreenConnect, showing the technique is not MSP360-specific; Microsoft provides IOCs, hunting queries, and mitigation guidance (Application Control, AppLocker publisher rules, ASR rules) but does not attribute the activity.
 microsoft.comwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security
- Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix
Huntress researchers document a campaign where attackers built a malicious ChatGPT Custom GPT ("Plus 5.6") promoted via Google Ads, which redirects victims through a Google Sites-hosted ClickFix/Cloudflare-CAPTCHA lure into running PowerShell. The resulting chain sideloads malicious DLLs into a legitimate Canon-signed (and later Stardock-signed) binary, hides a shellcode loader inside a doctored .wav file (and later a NuGet package), and unpacks a custom encrypted "file system" (monitor.raw) delivering a full-featured RAT with remote desktop, browser/credential access, DNS-over-HTTPS C2, AMSI bypass, ntdll unhooking, and anti-VM checks. Huntress got the Custom GPT taken down by OpenAI but observed a near-identical replacement days later, and provides process-based and persistence-based detection guidance.
huntress.comwriteupAdded 29 Sep 2026, published 28 Sep 2026🛡️ Security - The Not So Silent Miner: Threat Actor Compiles Cryptominer on the Endpoint
Huntress SOC analyzes an intrusion that began with exploitation of Samsung MagicINFO (CVE-2025-4632, after incomplete fix of CVE-2024-7399) via tomcat9.exe. The actor took three tries to install AnyDesk (certutil and PowerShell attempts were blocked by Defender), created an 'oldadministrator' account, disabled Defender, then ran Silent XMR Miner Builder, which compiled a Monero miner on the endpoint using csc.exe, cvtres.exe, donut, tcc and MinGW gcc. The miner ran masquerading as explorer.exe against C3Pool; the post gives command lines and detection ideas such as unusual compiler child processes from an unsigned parent and explorer.exe with mining arguments.
huntress.comwriteupPublished and added 24 Sep 2026🛡️ Security - Google Doc Sidebar Sends Mac and Windows Users Down Different Paths to Malware
Huntress SOC analysts Ryan Dowd and Jon Semon tore apart a live social-engineering campaign that began with a fake CoinDesk marketing exec DMing a researcher a Google Doc containing a container-bound Apps Script sidebar. The script ran client-side without OAuth consent, exfiltrated victim IP/geolocation/wallet presence via the Telegram API, then routed macOS users to a piped zsh/DMG AMOS stealer chain and Windows users through ClickOnce and PowerShell loaders using three stolen or fraudulent code-signing certificates (a Norwegian company, Discord, and Lenovo). The Windows chain culminated in NetSupport Manager RMM abuse, a Ledger wallet implant, and a self-generated rogue root certificate authority (spoofing Google Trust Services) installed via MsBuild.exe hollowing to silently intercept HTTPS traffic, which the authors flag as the artifact most likely to survive incident remediation short of full reimaging.
huntress.comwriteupAdded 11 Sep 2026, published 15 Sep 2026🛡️ Security  ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
Cisco Talos reconstructs two related WebDAV-based infection chains (tracked actor UAT-10820) that use a ClickFix fake-CAPTCHA lure, EtherHiding on BNB Smart Chain to stage JavaScript via a malicious Cloudflare Worker, and WebDAV-delivered disguised DLLs executed via rundll32 ordinal calls to drop the Amatera stealer. Depending on the C2 configuration, Amatera then deploys either a NativeAOT-loaded ZigCryptoStealer with a BYOVD EDR-killer driver and a Go-based Yamux reverse proxy, or a PowerShell stager that installs a trojanized NetSupport Manager RAT pointed at Russian C2 infrastructure. The post details loader internals, Amatera's dead-drop C2 resolution via Telegraph and Steam, and provides ClamAV signatures plus a full IOC list.
blog.talosintelligence.comwriteupAdded 7 Oct 2026, published 8 Sep 2026🛡️ Security- Daisy-Chaining Trust: Investigating Faronics Deploy Abuse | Huntress
Huntress details a phishing campaign that tricks victims into installing a legitimately signed Faronics Deploy agent disguised as Adobe/Zoom documents, enrolling endpoints into an attacker-controlled deployment console. The threat actors then abuse Faronics' remote script execution to pull PowerShell payloads (via curl, mshta, msiexec) from GitHub-hosted staging and install ScreenConnect for persistent remote access. The post identifies key forensic artifacts (C:\ProgramData\Faronics\Logs\ScriptRunner.log and the deployment's unique "ck" identifier) that defenders can use to trace attacker infrastructure and cluster malicious enrollments, and notes Faronics' response to disrupt abuse after Huntress's disclosure.
huntress.comwriteupAdded 5 Sep 2026, published 31 Aug 2026🛡️ Security - Bank of America Phishing Email Delivers ScreenConnect Malware
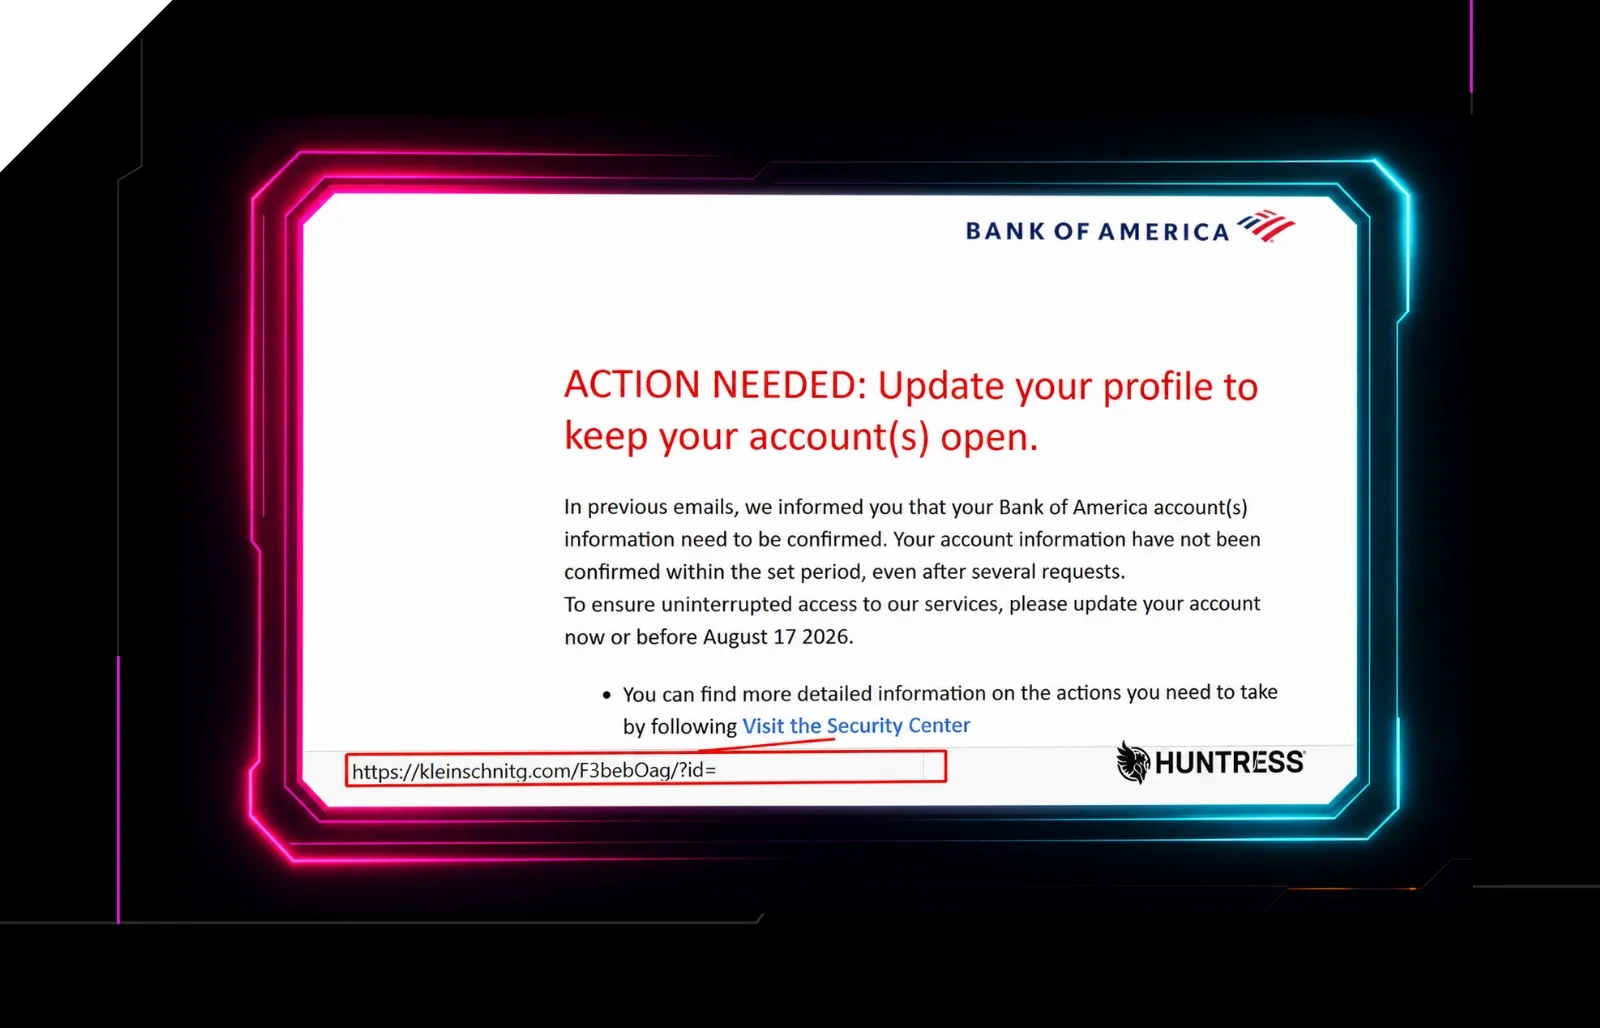
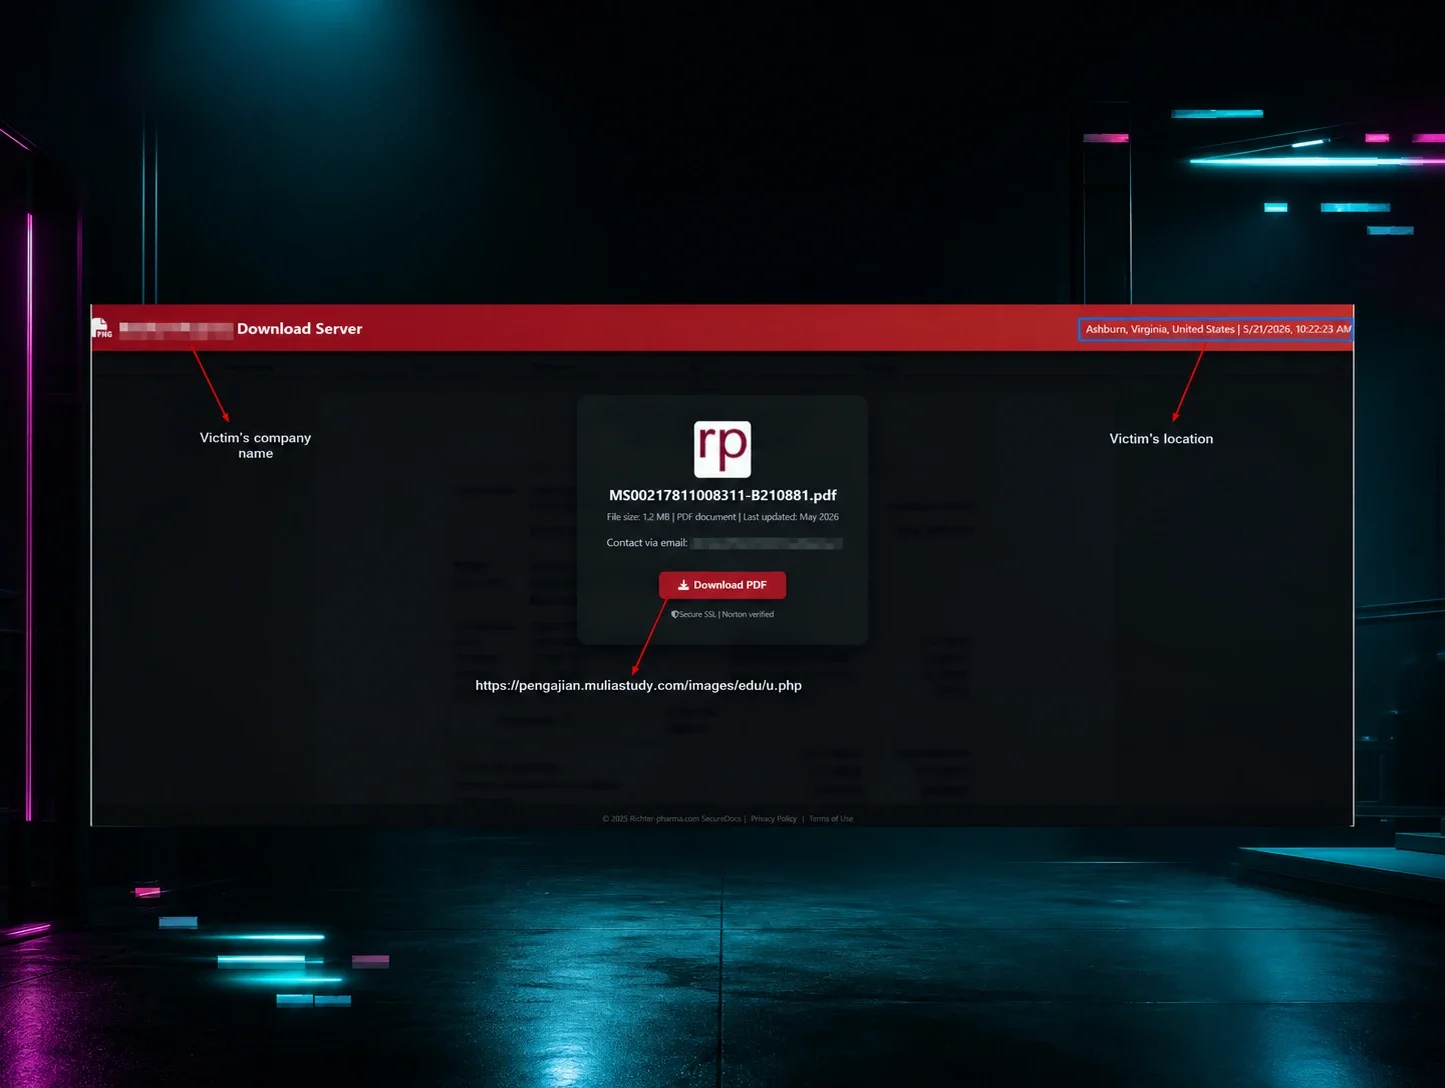
Huntress dissects a Bank of America-themed phishing email that lures victims into downloading AccountGuardSetup.vbs, which unpacks through several layers of base64-encoded PowerShell to silently install ScreenConnect RMM with Administrator privileges. The chain uses AES-128-CBC encrypted blobs to deliver a C# UAC-bypass exploit via the ICMLuaUtil COM interface (MITRE ATT&CK T1548.002), then hides the resulting ScreenConnect service (renamed "Windows Security") from users and admins using SDDL/ACL manipulation so it can't be seen, logged, or removed.
huntress.comwriteupAdded 3 Sep 2026, published 4 Aug 2026🛡️ Security  Socket: Fake Corepack Site Distributes Infostealer and Proxyware to Developers
Socket's Threat Research team analyzed corepack[.]org, a fake site impersonating the Node.js Corepack tool that exploits its 2025 removal from Node.js bundling to rank in search results and trick developers into downloading a fake VPN installer. The installer drops OpenShield (an infostealer with browser-data/SSH-key theft, PowerShell execution, and run-key persistence) plus a bandwidth-sharing proxyware component that turns victim machines into proxy exit nodes, while a second click path delivers adware/trojan activity via OperaGXSetup.exe. The post includes full IOCs and details community/OpenJS Foundation takedown efforts against the domain.
 socket.devwriteupPublished and added 25 Jul 2026🛡️ Security
 SleeperGem: RubyGems supply chain attack targets dormant maintainer accounts
Aikido researchers dissect SleeperGem, a RubyGems supply chain attack where a newly published gem, git_credential_manager, downloaded malicious binaries hosted on a fake git-ecosystem account at git.disroot.org and executed them via shell or PowerShell. The attacker evolved the payload across four versions in nine hours, silencing output, wiring execution into the gems require and load path, and adding a check to skip roughly 30 CI environment variables so it only fires on developer laptops, then used two separate long-dormant maintainer accounts to push the gem as a dependency into the trusted gems Dendreo and fastlane-plugin-run_tests_firebase_testlab with over 574000 downloads. The piece argues this is RubyGems first taste of the dormant-maintainer-account-takeover pattern long seen on npm and PyPI.
 aikido.devwriteupAdded 3 Sep 2026, published 19 Jul 2026🛡️ Security
 FauxUV campaign (Xygeni)
Xygeni details FauxUV, a cluster of PyPI packages (moon-uv, my-magic-uv-helper) that impersonate the popular Rust-based Python package manager uv but carry almost no real functionality. Instead, on Windows they launch JupyterLab with authentication disabled (empty token, bound to 0.0.0.0, XSRF checks off) and, in later versions, expose it to the internet via a Pinggy SSH reverse tunnel, turning a legitimate data-science tool into an open remote shell that inherits the installing user's credentials. The writeup traces the install-time PowerShell trigger moving from setup.py to a separate CLI tool across versions and provides IOCs and detection guidance.
 xygeni.iowriteupPublished and added 18 Jul 2026🛡️ Security
 Socket: Operation Muck and Load
Socket details "Operation Muck and Load," a campaign starting with a malicious Go module (github.com/kaleidora/dnsub-scanning-tool) that impersonates a DNS scanner but launches hidden PowerShell to fetch and decode a multi-layer, XOR-encrypted loader. The loader resolves encrypted payload locations from public dead drops (Pastebin, GitHub, YouTube, Instagram, Telegram, Google Docs), retrieves a password-protected .7z archive masquerading as Microsoft Photos, and deploys AsyncRAT/Quasar/Remcos-style RATs and Vidar infostealer. Pivoting from the module, Socket uncovered 222 GitHub repositories across 190 accounts using automated force-push workflows tied to a single email (ischhfd83@rambler.ru) to fake activity and credibility, some directly hosting Vidar, XMRig/BitMiner, and trojan loaders.
socket.devwriteupPublished and added 16 Jul 2026🛡️ Security- Threat Actors Achieve Persistence After SQL Injection
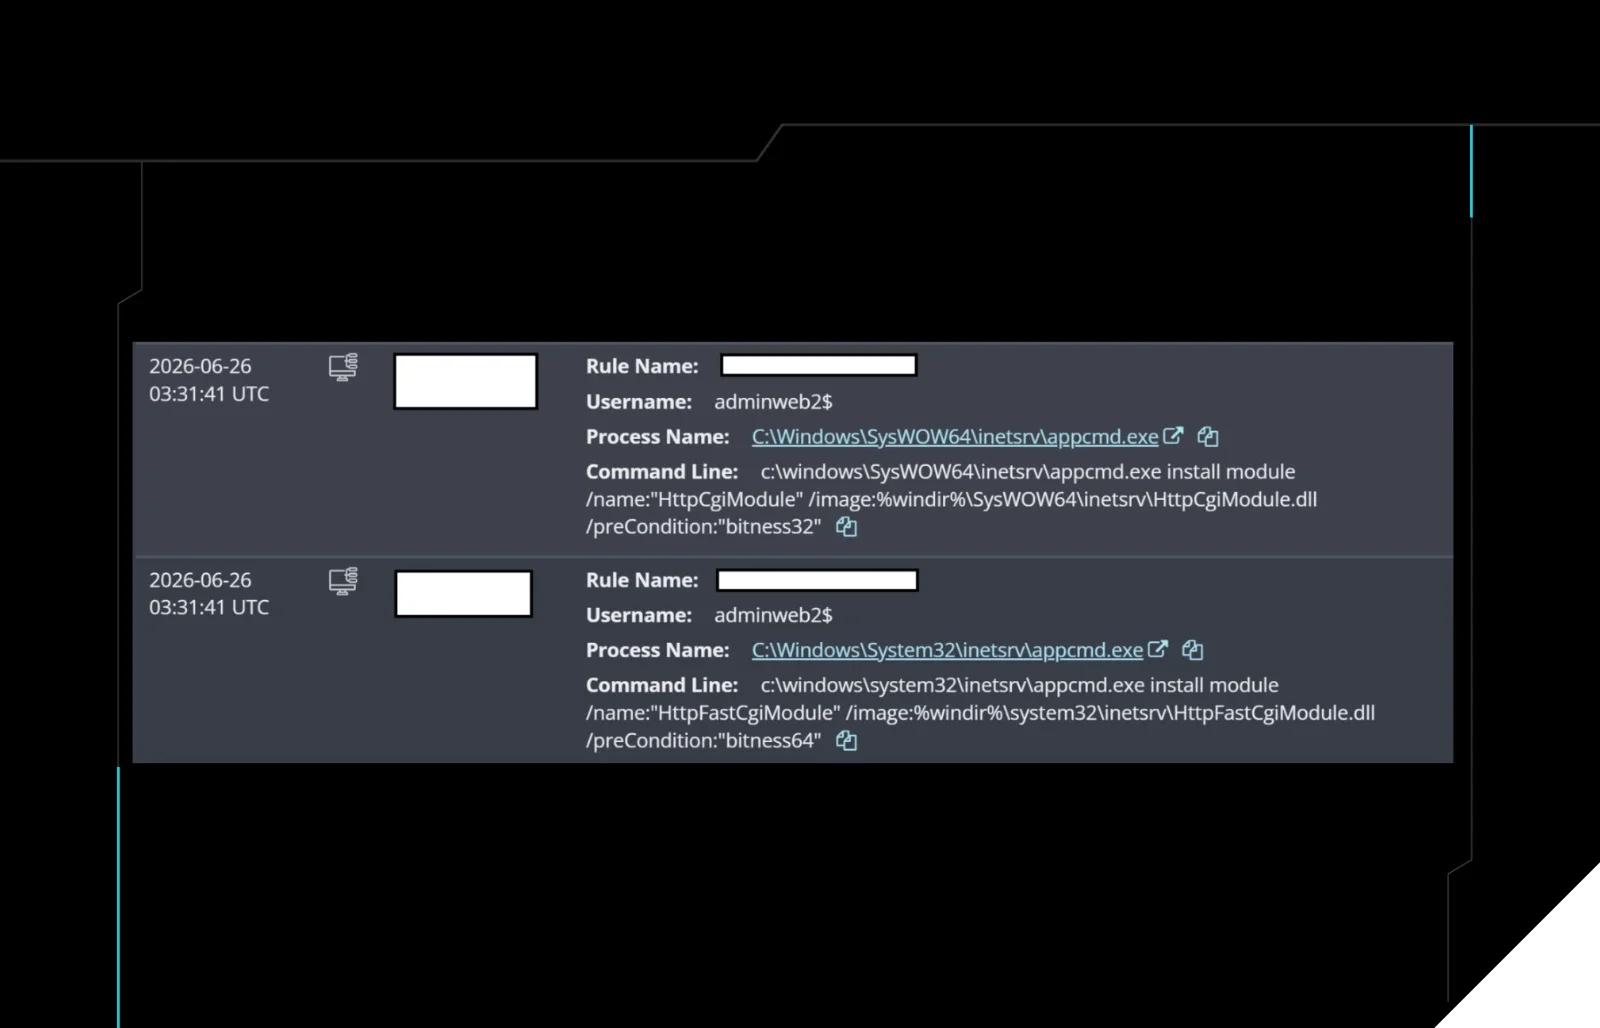
Huntress SOC analysis of a June incident where a threat actor exploited a SQL injection flaw in an IIS/MSSQL web application to gain access, then extensively modified the environment: enabling Terminal Services, creating a rogue admin account (adminweb2$), disabling Windows Defender, deploying BadIIS malicious IIS modules (HttpFastCgiModule.dll, HttpCgiModule.dll) for SEO fraud, installing the XMRig cryptominer with nssm.exe persistence and hidden/system file attributes, and dropping additional PowerShell/batch payloads (qdcjoke1.2.ps1, c_joke1.2.ps1) via base64-encoded PowerShell and Out-of-Band Application Security Testing (OAST) exfiltration channels (oastify.com).
huntress.comwriteupAdded 3 Sep 2026, published 13 Jul 2026🛡️ Security - AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress
Huntress recovered and reconstructed "Untitled1.ps1," a PowerShell Active Directory enumeration script used by an attacker during a June 3 incident via RDP access with compromised credentials, and identified it as AI-generated ("vibe-coded") based on artifacts like an unedited LLM placeholder hostname, a "FULLY FIXED" prompt-iteration title, over-engineered five-method DC-discovery fallback logic, and gratuitous colored console/HTML reporting output. The attack chain paired this bespoke recon tool with off-the-shelf abuse of s5cmd (legitimate AWS S3 CLI used for exfiltration) and SharpShares (share enumeration), illustrating how LLM-generated one-off malware evades hash/signature-based detection and pushes defenders toward behavioral analytics on Active Directory enumeration patterns.
huntress.comwriteupAdded 3 Sep 2026, published 8 Jul 2026🛡️ Security - Fantastic clear-text passwords and where to collect them (Part 2 - Windows)
A DFIR.ch deep-dive on stealthier alternatives to LSASS dumping for harvesting Windows cleartext credentials, covering WDigest re-enablement, PowerShell ConsoleHost_history.txt, AD user-attribute leaks, Group Policy Preferences (GPP) cPassword, and rogue Security Support Provider (SSP), Password Filter DLL, and Network Provider DLL registration. Each technique is illustrated with real incident-response case data (registry commands, malicious DLL names like kerberos_sp.dll and mimilib.dll, and exfiltrated log paths), paired with Sysmon Event ID 13/11 detection guidance and hardening recommendations (disabling custom SSPs, Protected Event Logging).
dfir.chwriteupAdded 3 Sep 2026, published 28 Jun 2026🛡️ Security - From Code to Coverage (Part 6): What netlogon.log Sees That Event 1644 Never Will
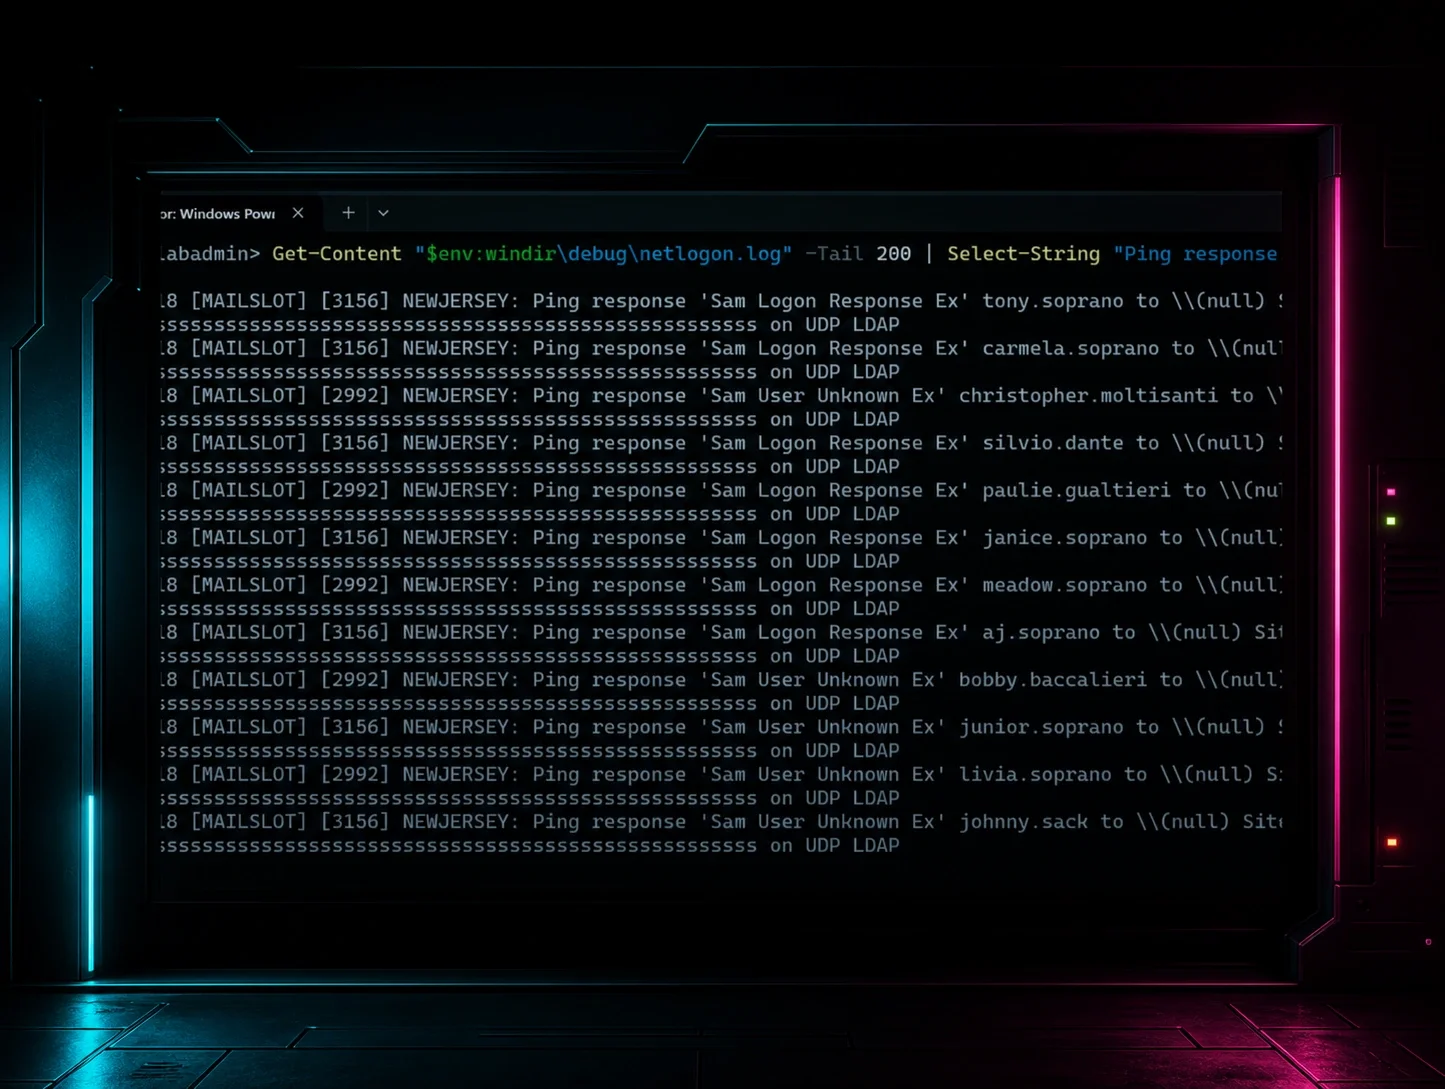
Part 6 of Huntress's "From Code to Coverage" series reverse-engineers ldapnomnom's LDAP Ping (cLDAP-style) Active Directory username enumeration technique, tracing its Go source down to the Windows Filtering Platform to test the tool's claim of generating "no Windows audit logs." Lab testing shows Event 1644 never fires for LDAP Ping (it's processed by netlogon.dll, not the ntdsa.dll LDAP engine it monitors), but netlogon.log captures every queried username including disabled-account detail attackers can't see, while Event 5156 attributes source IP for ldapnomnom's TCP connections — a gap that disappears entirely if an attacker switches to true UDP cLDAP (as demonstrated with a custom cldap_ping.py), leaving only MDI's threshold-based external ID 2437 as network-layer coverage. The piece also audits the ldeep tool's enum_users transport and provides a PowerShell correlation script joining netlogon.log and Event 5156 within a 5-second window.
huntress.comwriteupAdded 3 Sep 2026, published 24 Jun 2026🛡️ Security  A Forgotten Contributor Account Compromised the Entire Mastra npm Package Scope
Snyk details how a dormant, never-revoked npm contributor account (ehindero) was used to republish the entire @mastra scope (142+ packages, ~4M monthly downloads for @mastra/core alone) with an injected dependency, easy-day-js, a byte-for-byte dayjs impersonator. The postinstall hook in easy-day-js@1.11.22 disables TLS verification, pulls a second-stage payload from a raw IP, and drops a cross-platform cryptocurrency wallet stealer plus a RAT with OS-specific persistence (LaunchAgent, systemd unit, PowerShell staging) that beacons every 10 minutes over a self-signed wolfSSL certificate. The piece covers detection steps, the Snyk advisory (SNYK-JS-EASYDAYJS-17353313), and draws parallels to the earlier Axios npm compromise attributed by Microsoft to Sapphire Sleet (BlueNoroff).
 snyk.iowriteupAdded 3 Sep 2026, published 16 Jun 2026🛡️ Security
- Potemkin Loader & RMMProject The Anatomy of a ClickFix Attack
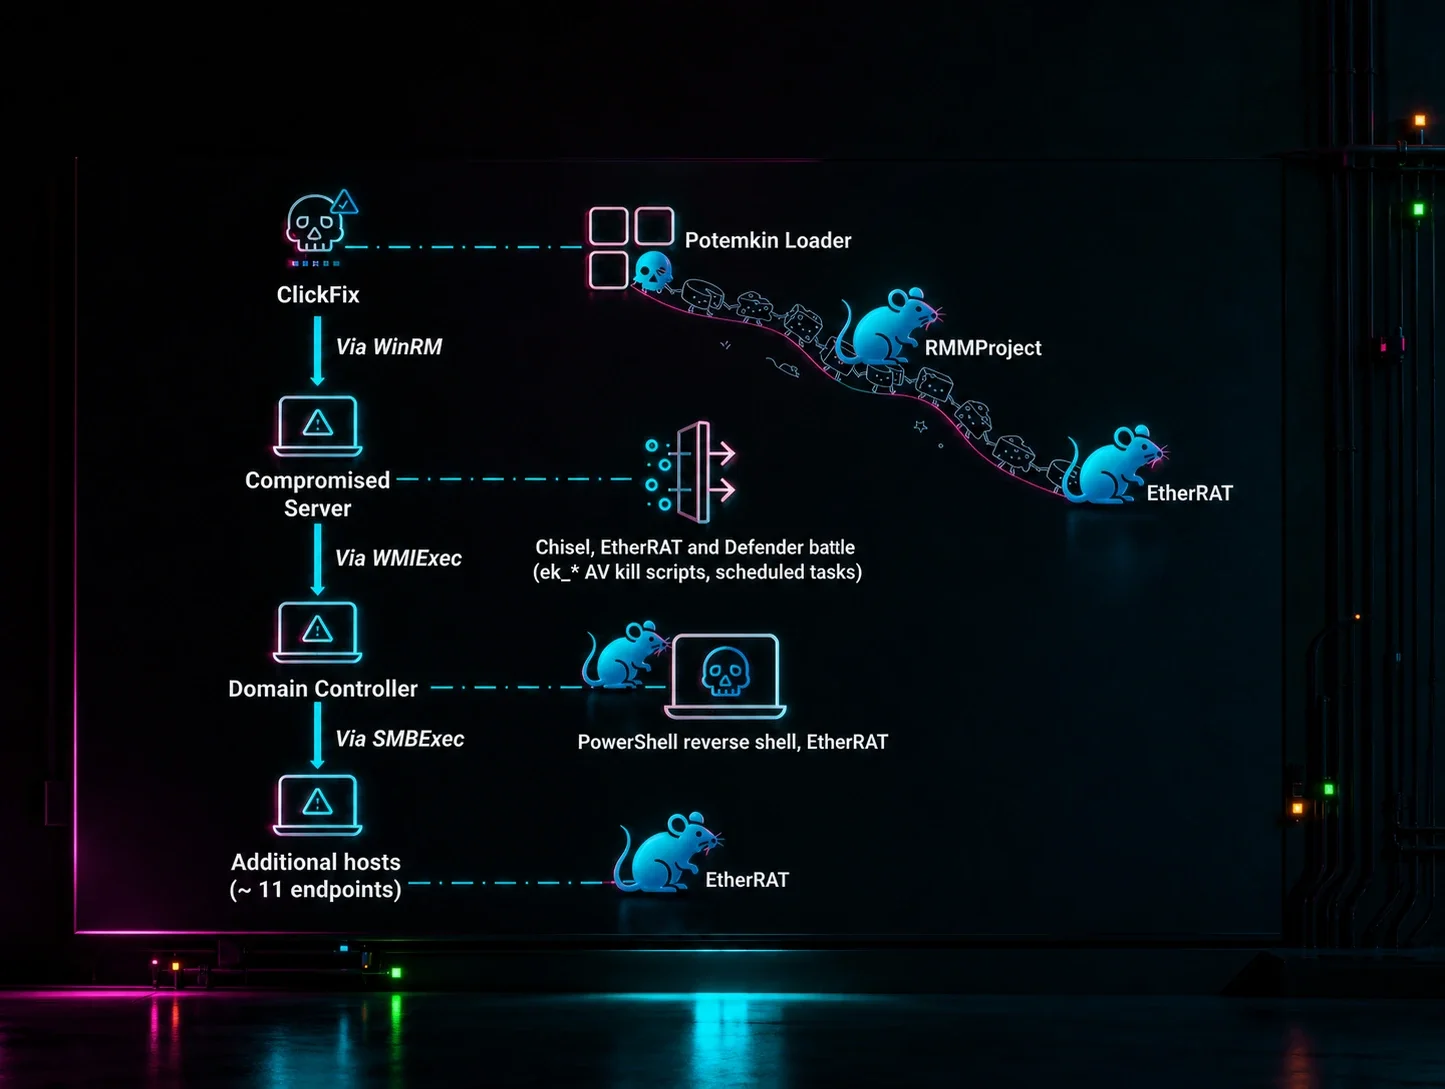
Huntress tears down a May 2026 ClickFix intrusion that escalated from a single unmonitored endpoint to hands-on-keyboard compromise of 11 hosts. The chain starts with a pcalua.exe/mshta.exe LOLBIN abuse to run a remote HTA that silently installs an MSI, dropping Potemkin, a custom x64 DGA-based loader (XorShift32 seed 151678, custom byte cipher, reflective in-memory DLL loading), which fetches RMMProject, a 4.4MB LuaJIT-scriptable module with 15 task types including Chrome App-Bound Encryption bypass via DLL injection into Chrome's IElevator COM interface, Firefox NSS credential theft, and a hidden-desktop remote-control (RTSC) module. The attackers also deployed EtherRAT (an EtherHiding Node.js backdoor resolving C2 from an Ethereum smart contract) and a renamed Cloudflare tunnel client, then moved laterally via WMIExec/SMBExec/WinRM with an AMSI-bypass PowerShell loader to reach the domain controller.
huntress.comwriteupAdded 3 Sep 2026, published 16 Jun 2026🛡️ Security - Inside .NET Loader Analysis: From Malspam to In-Memory Loader
Huntress SOC dissects a multi-stage infection chain that begins with a malspam HTML attachment routed through a legitimate Google DoubleClick tracking link to evade reputation filters, before landing on a self-personalizing phishing kit and dropping a ZIP with a heavily obfuscated JScript loader. The chain cascades through PowerShell droppers into a .NET stager that performs extensive anti-analysis/anti-sandbox checks, disables Windows Defender, patches AMSI (via NtManageHotPatch on Windows 11 24H2) and ETW at the native API level, and uses RunPE process hollowing into InstallUtil.exe or MSBuild.exe to run a final loader that communicates over AES/RSA-encrypted, protobuf-serialized TCP C2 with certificate pinning. The writeup includes GPU-fingerprinting behavior, persistence via registry Run keys and randomized scheduled tasks, and concrete detection/hardening recommendations.
huntress.comwriteupAdded 3 Sep 2026, published 3 Jun 2026🛡️ Security - The Gentleman Ransomware | Defense Evasion TTPs Uncovered | Huntress
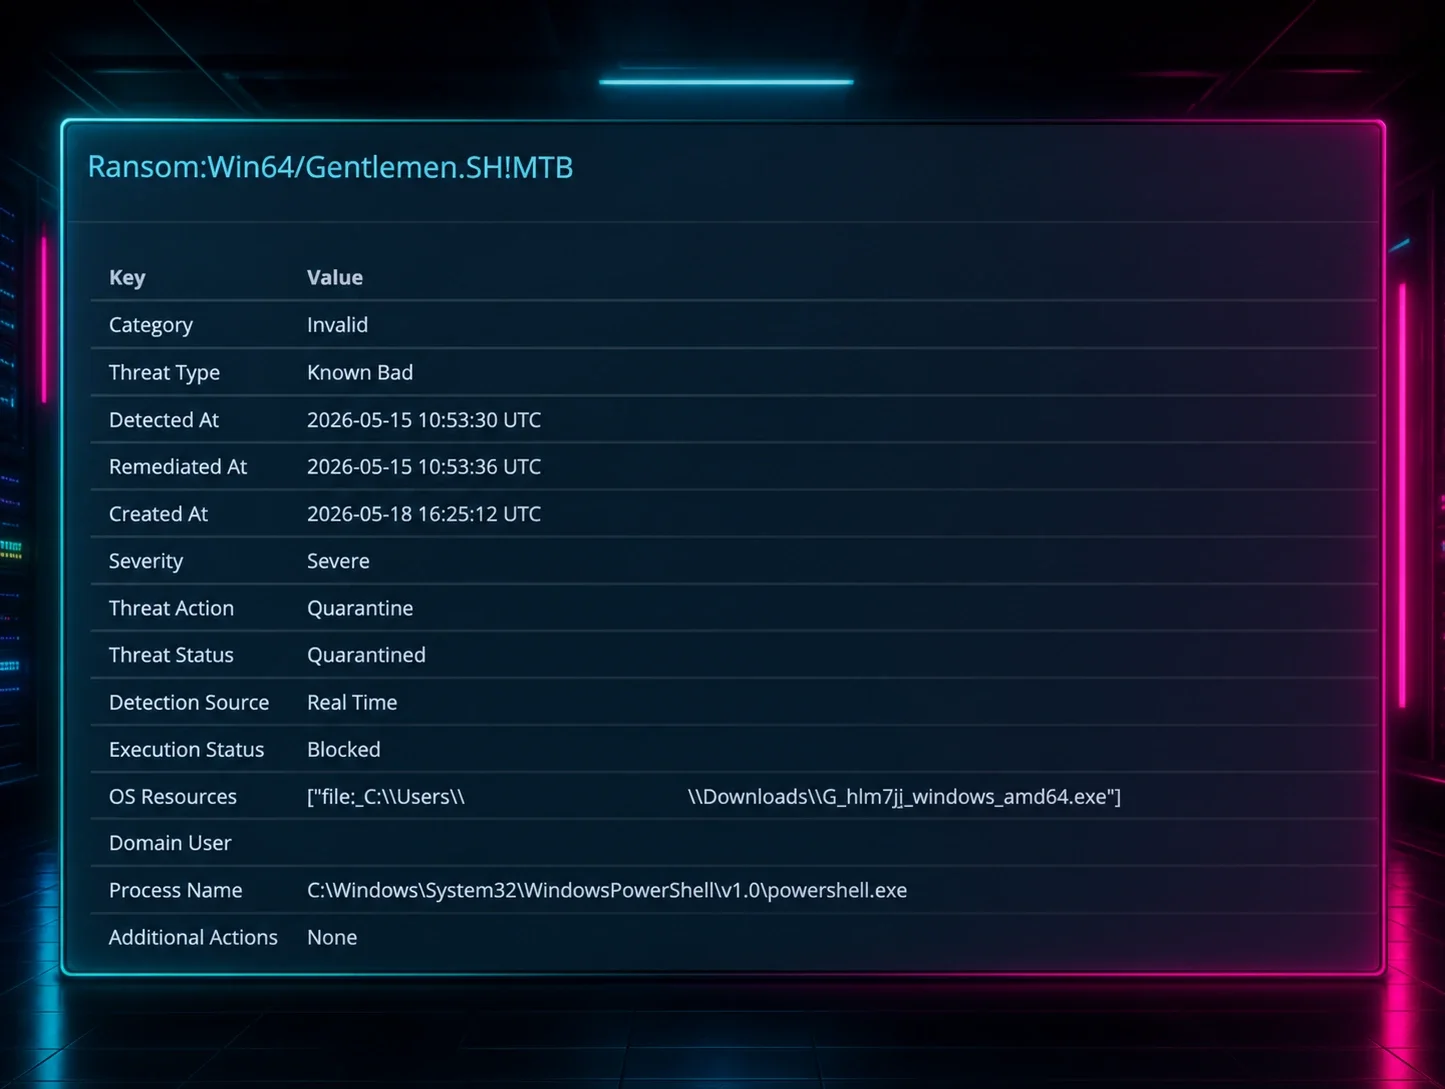
Huntress SOC details two Gentlemen ransomware incidents showing Windows Event Log clearing, PowerShell-based Defender tampering, and Scheduled Task persistence via a fake svchost32.exe creating a SOCKS proxy C2 connection. Ties findings to a leaked internal RaaS database revealing CVE-2024-55591 exploitation and infrastructure links to Qilin and Lazarus Group.
huntress.comwriteupAdded 3 Sep 2026, published 21 May 2026🛡️ Security - The 60ms Window: How Event 5156 Solves the ADWS Attribution Problem
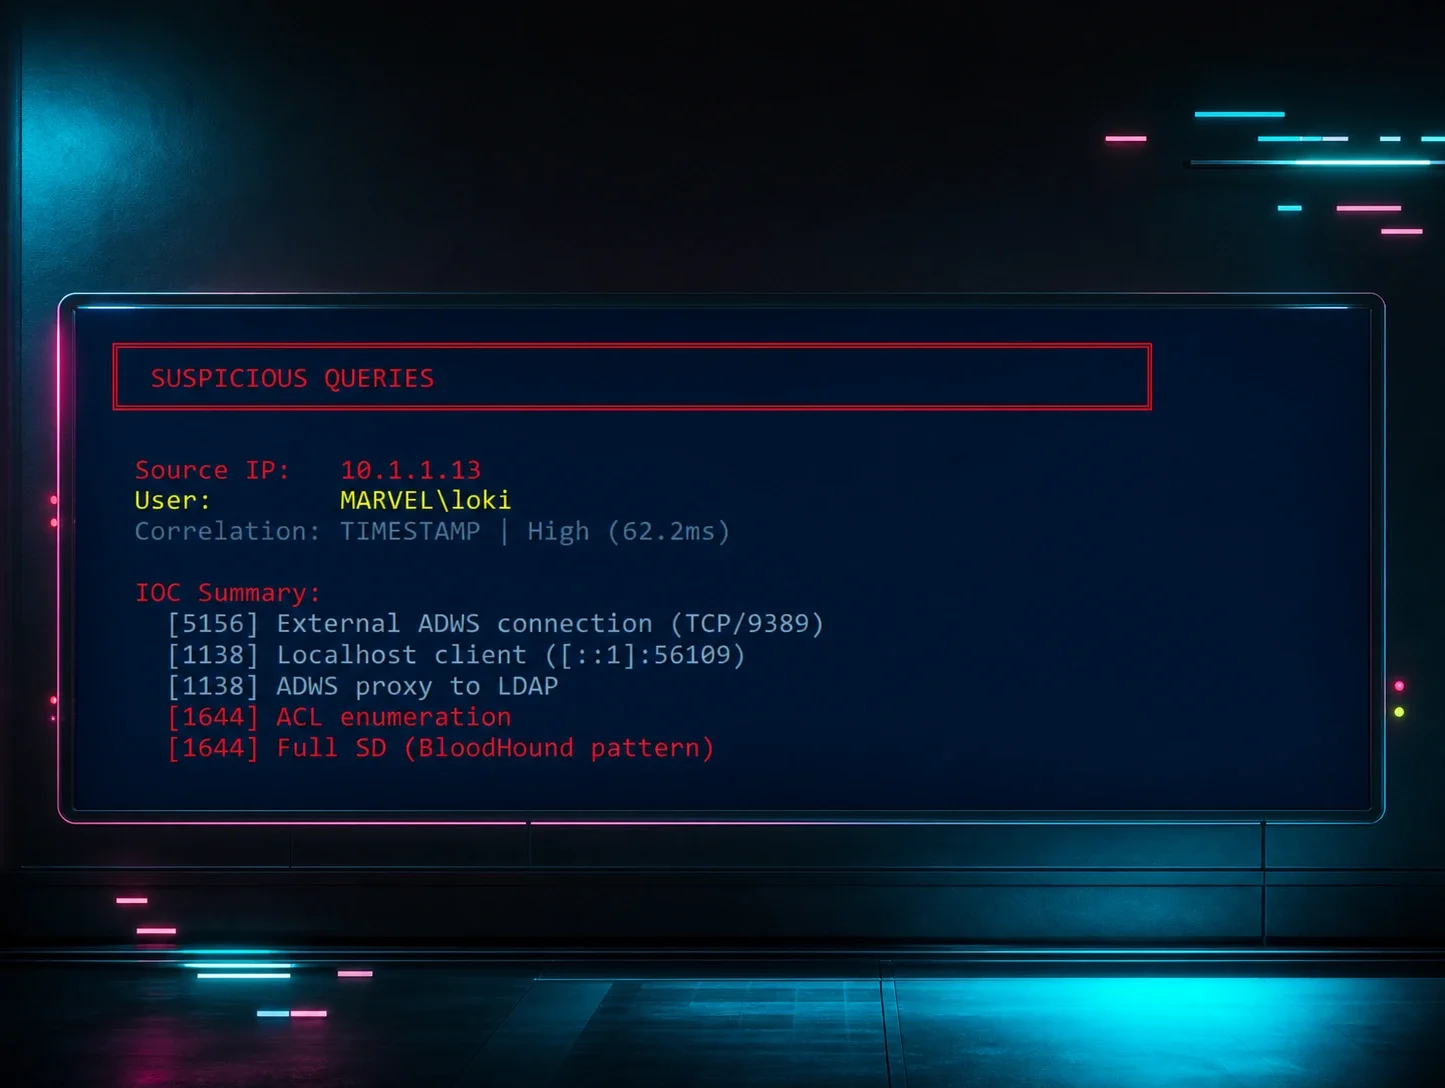
Huntress researchers solve the long-standing 'ADWS attribution problem' where tools like SOAPy abuse Active Directory Web Services to hide the attacker's real source IP behind localhost ([::1]) in LDAP diagnostic logging (Event 1644). By correlating Windows Filtering Platform Event 5156 (which captures the real inbound source IP on port 9389 before ADWS proxies to loopback) with Event 1138 (ADWS session) and Event 1644 (LDAP query) using a stable ~60-80ms timestamp window, they demonstrate reliable attribution even when port-based correlation fails due to log rollover. The post includes a released PowerShell script (Get-ADWSAttribution.ps1) and addresses the false-positive concern of RSAT tools also using ADWS via pattern detection on suspicious 1644 query attributes.
huntress.comwriteupAdded 3 Sep 2026, published 9 Apr 2026🛡️ Security - The ADWS Architecture That Hides PowerShell AD Enumeration
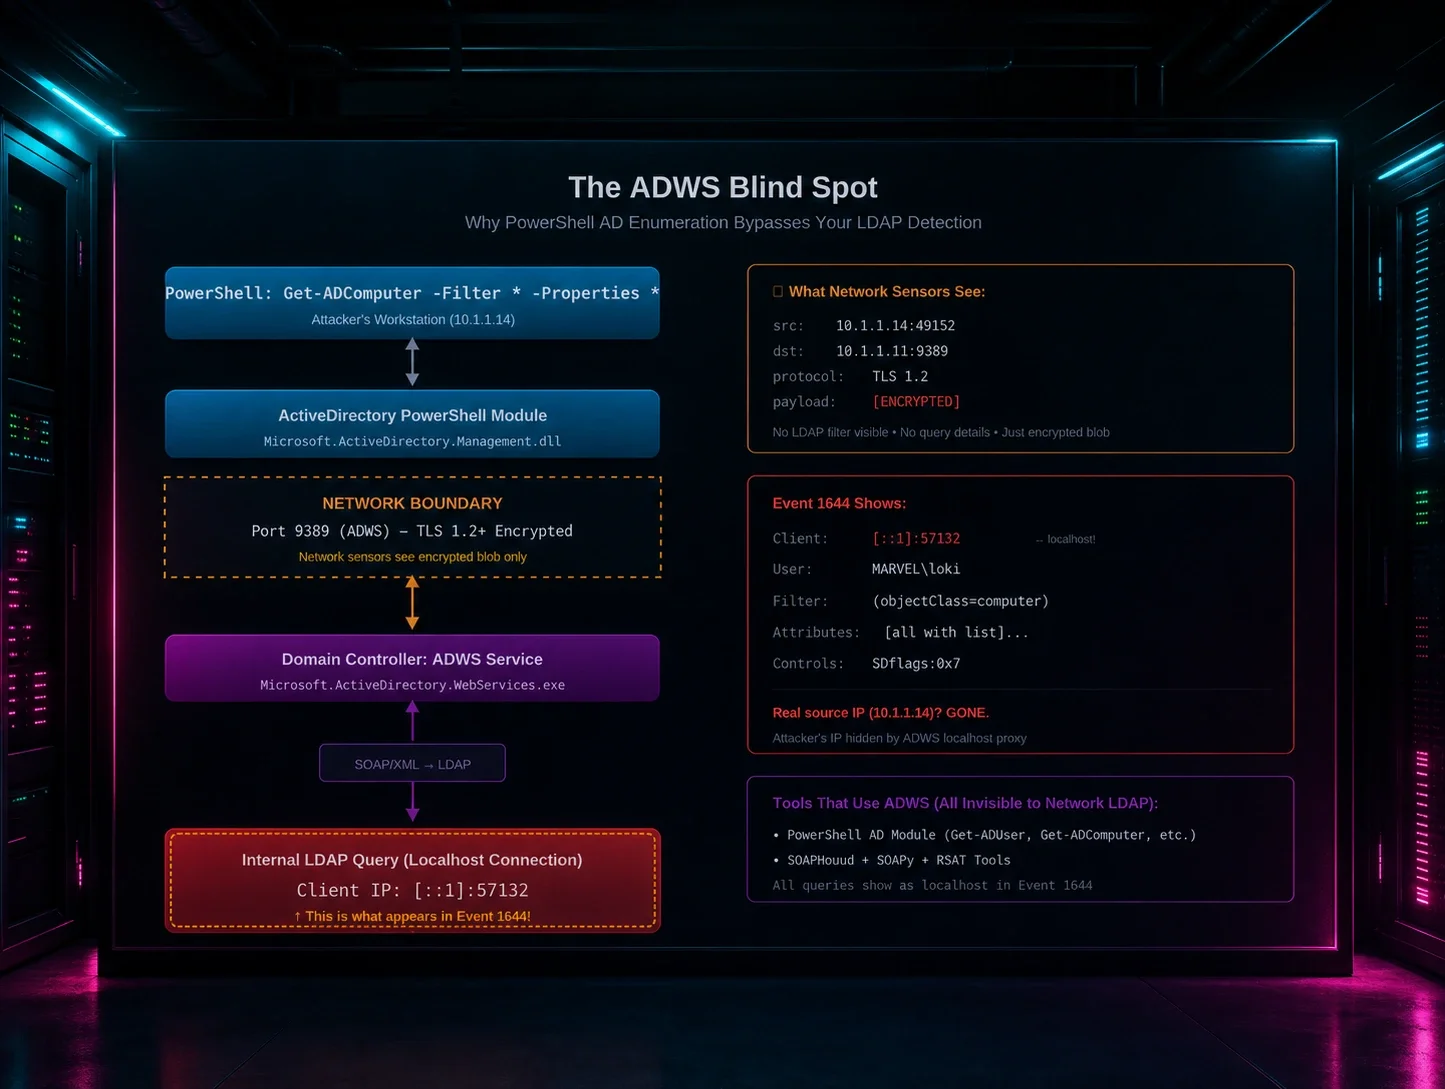
Part 5A of Huntress's LDAP/AD detection series explains why native PowerShell commands like Get-ADComputer -Properties * evade traditional LDAP-based detections: PowerShell's ActiveDirectory module uses Active Directory Web Services (ADWS) over encrypted SOAP on port 9389 rather than LDAP on 389/636, and the resulting Event 1644 log shows the query originating from localhost ([::1]) instead of the attacker's real IP. The author shows how to correlate Event 1644 with ADWS connection/session events (1138, 1139, 1166, 1167) via shared Operation ID to reconstruct full enumeration sessions, and flags the "[all_with_list]" attribute prefix and "SDflags:0x7" server control as high-fidelity indicators of PowerShell bulk property/security-descriptor dumps (as used by tools like BloodHound). It also demonstrates that case obfuscation of cmdlets (e.g., geT-aDcompUTER) is irrelevant at the LDAP layer since PowerShell is case-insensitive and translates to standard LDAP filters before reaching the DC.
huntress.comwriteupAdded 3 Sep 2026, published 8 Apr 2026🛡️ Security










Showing 30 of 51
Show more