huntress.comwriteup🛡️ Security
M365 Token Spray and Replay Campaign Compromises Business Email Accounts
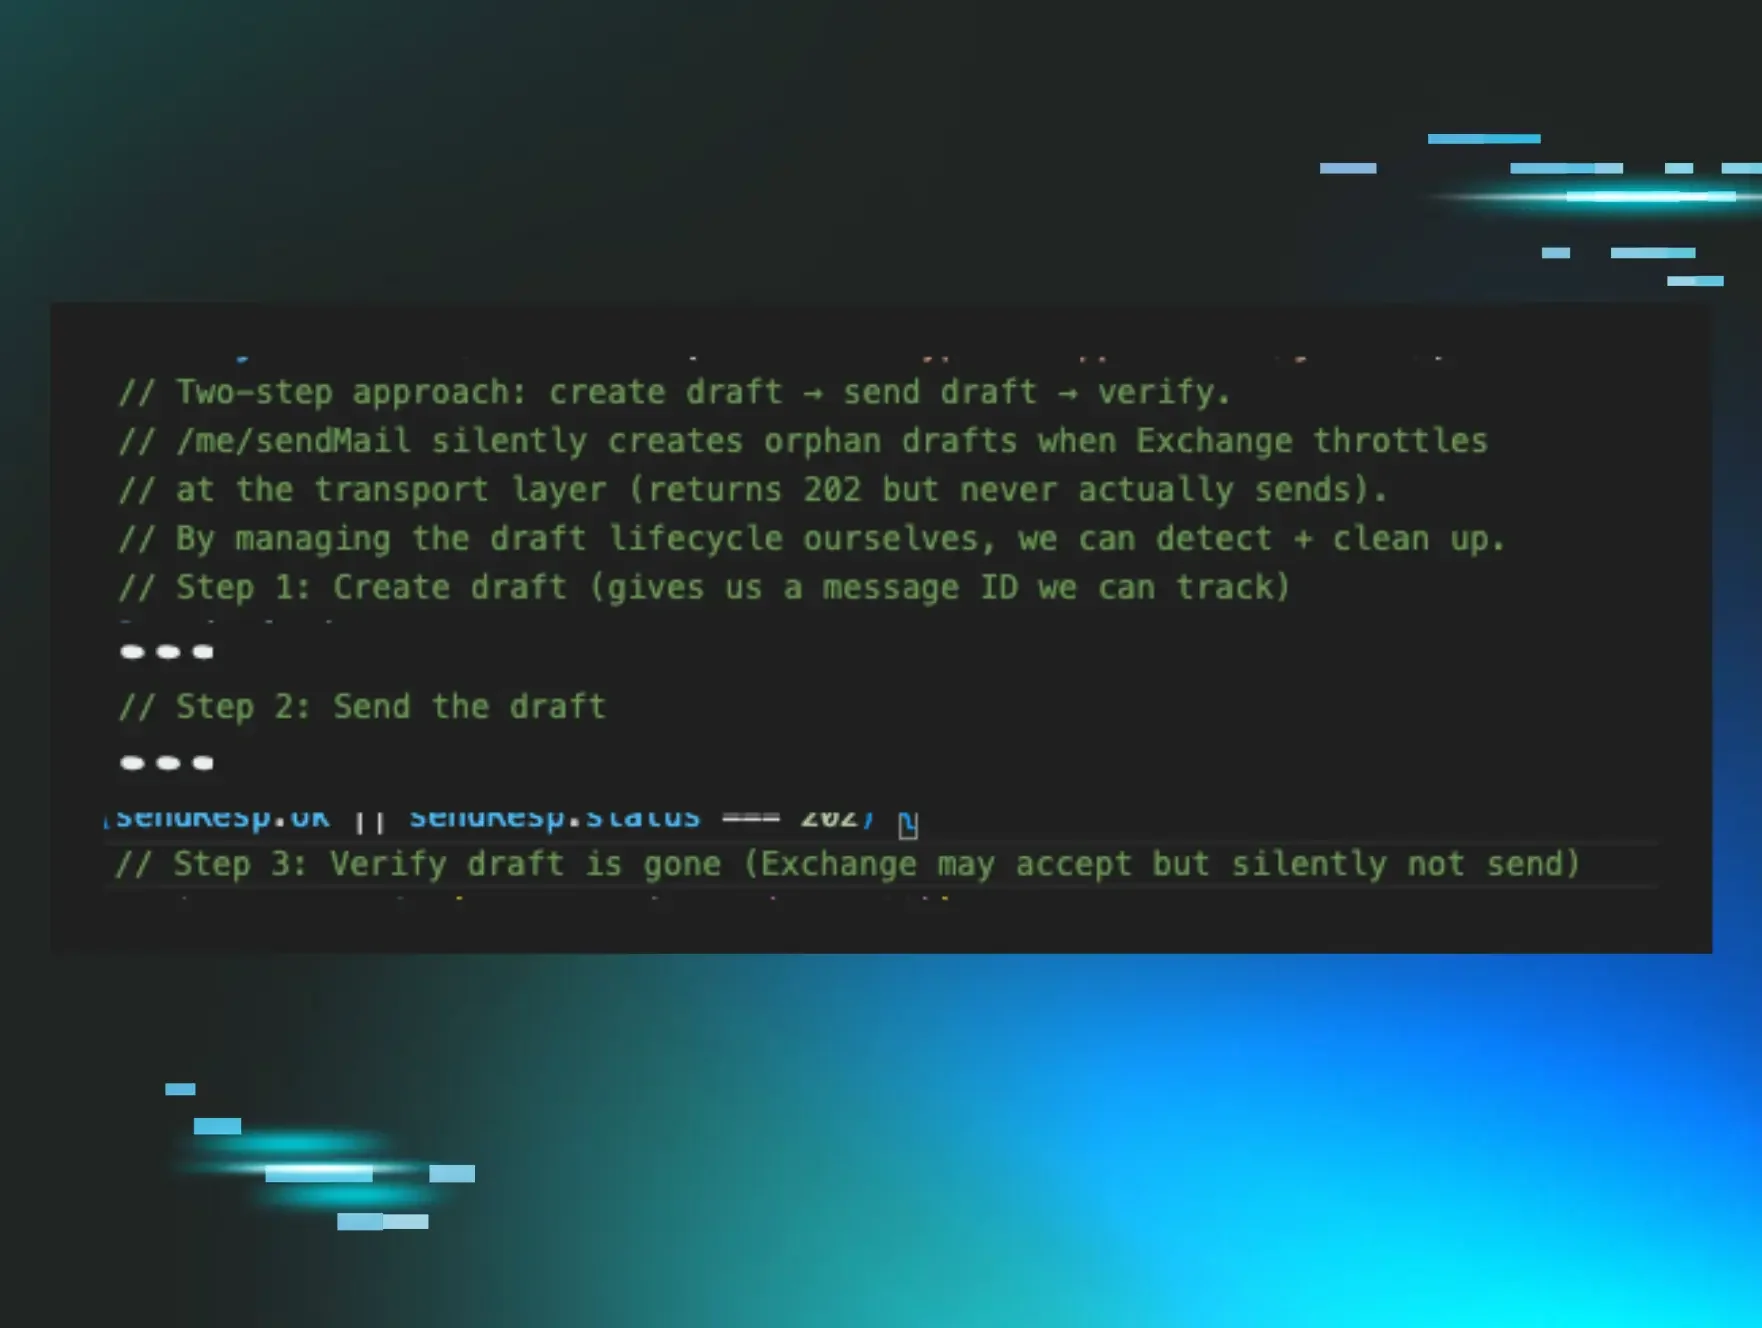
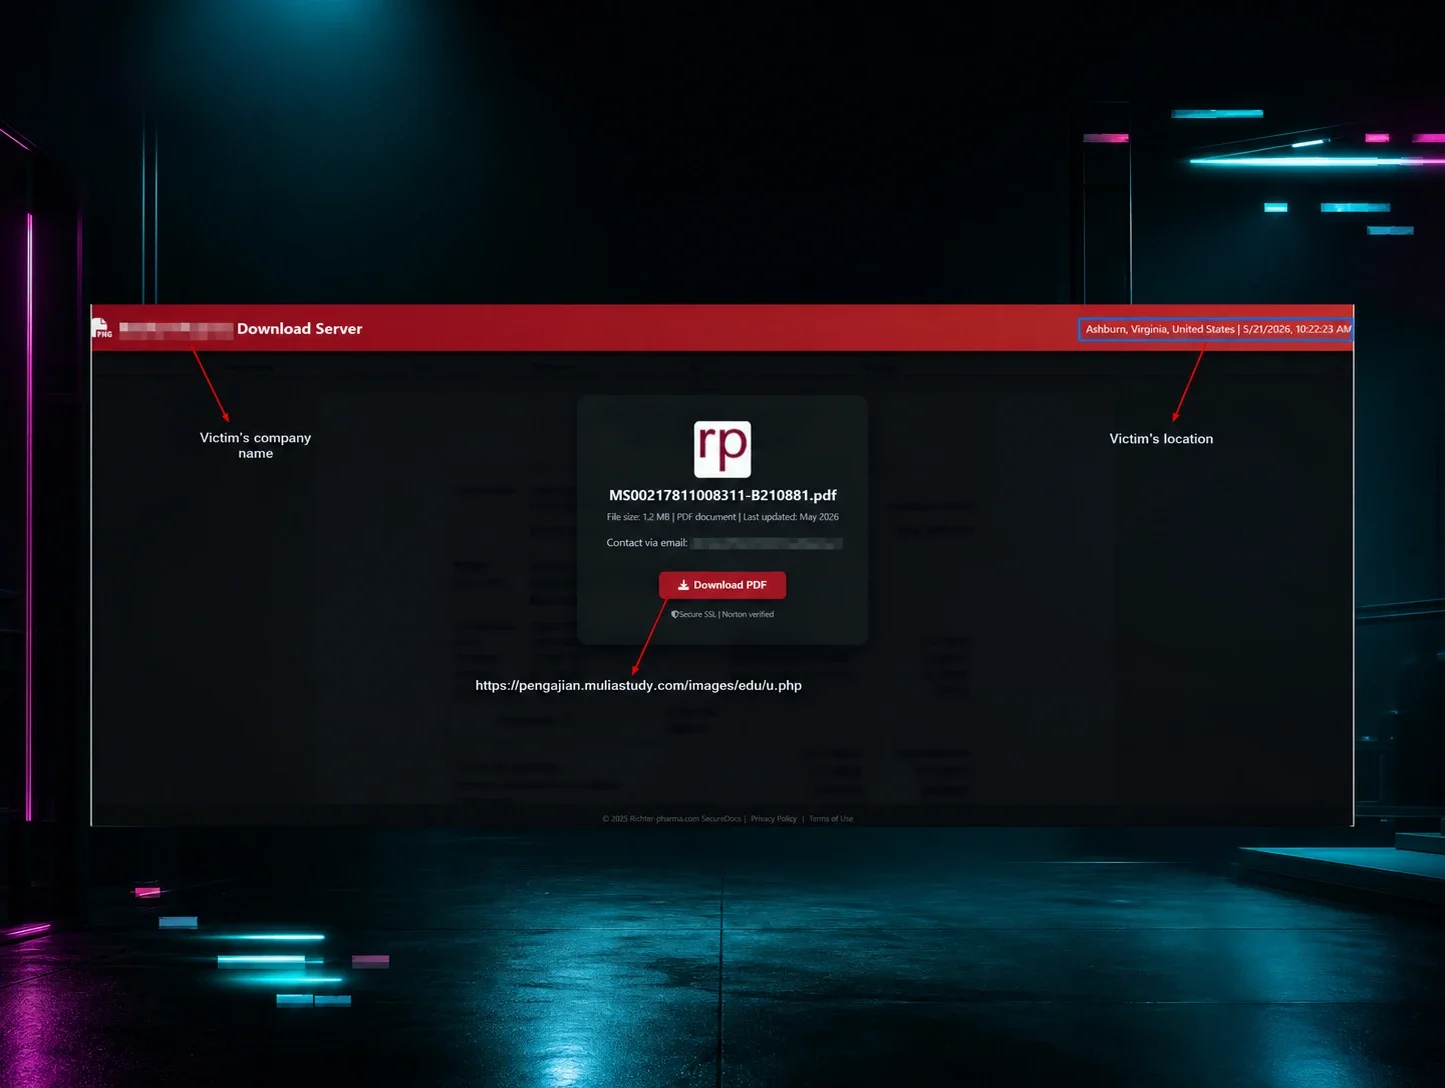
Huntress analysis of a July to September 2026 token replay ("token spraying") campaign: 497 successful Microsoft 365 sign-ins across 79 organizations, replayed from six addresses in 193.26.115.0/24 (1337 Services GmbH). Tokens came from AiTM relays, device-code phishing and social engineering. It covers four phases, rogue Entra devices, MFA method swaps, hidden inbox rules, hunting queries and Conditional Access guidance.
Microsoft 365Microsoft Entra IDConditional Access+3
token sprayingtoken replayadversary-in-the-middle+9
Threat Intel, Blue Team & Detection, Identity & Access· Published and added 22 Oct 2026