 Over 1,000 GitLab servers vulnerable to ongoing RCE attacks
CVE-2026-97229 is a maximum-severity integer overflow in GitLab's CI/CD Regular Expression Compiler that lets an unauthenticated attacker run code via a crafted regex in pipeline configuration. GitLab patched it on 12 October 2026 in versions 19.4.2, 19.3.5 and 19.2.8. CISA added it to KEV, and Shadowserver tracks over 1,000 unpatched servers, plus 11,300 exposed to the related CVE-2026-110264.
 bleepingcomputer.comarticlePublished and added 2 Nov 2026🛡️ Security
 Backporting security fixes at scale with Codex
Trail of Bits describes a Codex (GPT-5.6) workflow that backports security fixes to stable Linux kernel trees, Ubuntu LTS and Fedora. By 29 October 2026 it had helped land fixes for 149 CVEs in stable kernels. Agents find missing fixes, adapt patches and assemble validation evidence; a human review takes about 30 minutes to 3 hours. It also sizes the unfixed-CVE backlog in kernel branches, Debian 13 and Ubuntu 26.04.
 blog.trailofbits.comarticlePublished and added 2 Nov 2026🛡️ Security
- Backporting security fixes at scale with Codex
Trail of Bits describes a Codex agent workflow that backports security fixes to stable Linux kernel trees and distro packages. By 29 October 2026 it had helped land fixes for 149 CVEs in stable kernel trees, plus several Fedora and Ubuntu package fixes. Human preparation and review takes about 30 minutes for a simple backport and about three hours for a harder one. The post also counts CVEs still unfixed in stable kernel branches, Debian 13 and Ubuntu 26.04.
blog.trailofbits.comarticlePublished and added 2 Nov 2026🧠 AI  Alpine Linux rebuilds GitLab after attempted RCE attack
Alpine Linux rebuilt its GitLab server and reset all passwords after attackers tried to exploit CVE-2026-97229, a maximum-severity integer overflow in the Onigmo regex engine bundled with Ruby, on October 20-21. Eight worker crashes occurred and four were partially successful. Missing logs and outbound connection records meant compromise could not be ruled out. Alpine had run GitLab 19.3.4, then 19.3.6, which lacked the Ruby patch; the fixed image is alpinelinux/gitlab:19.3.6 with Ruby 3.3.13.
bleepingcomputer.comarticlePublished and added 1 Nov 2026🛡️ Security In Other News: Anthropic Breach Dispute, UEFI Flaw Hits Most Servers, Cloudflare AI Data Leak
SecurityWeek's weekly roundup of 30 October 2026 covers CVE-2026-97631, a 16-year-old buffer overflow in TianoCore EDK II that affects PXE network boot on most servers. It also covers a Cloudflare Workers AI cross-tenant leak caused by an SGLang bug, Anthropic's dispute with Cathedral over a bug bounty intrusion, and fake AI bots probing for secrets. Other items include AI-assisted ransomware (Gold Ogre, Aur0ra), the NIK C2 framework, and North Korean IT worker sanctions.
 securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security
 CISA says max severity GitLab flaw now exploited in the wild
CVE-2026-97229 is a maximum-severity GitLab flaw in the CI/CD Regular Expression Compiler, caused by an integer overflow, that lets unauthenticated attackers run code via a crafted regular expression. CISA added it to the KEV Catalog and ordered federal agencies to patch under BOD 26-04. GitLab fixed it in CE/EE 19.4.2, 19.3.5 and 19.2.8, and Shadowserver tracks about 2,800 exposed CE instances.
bleepingcomputer.comarticlePublished and added 30 Oct 2026🛡️ Security TeamViewer Flaw Could Let Malicious Hosts Take Over Support Technicians’ Machines
CVE-2026-111585 (CVSS 8.8) is an integer overflow in the remote-control screen processing of TeamViewer clients on Windows, macOS, Linux and Android. A malicious or compromised host can announce an oversized screen surface (for example 32768 by 32768 at 32 bpp), forcing a software decode path and an out-of-bounds write that crashes the viewer or runs code. Remedio's research shows a pointer overwrite routed to WinExec. Version 15.83 fixes it, along with CVE-2026-92372, CVE-2026-92374 and six local privilege escalation bugs.
securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security Inside mobile taint analysis: how source-to-sink tracking finds real data-leak paths | Oversecured Blog
Oversecured explains taint analysis for Android and iOS apps and contrasts it with pattern-matching SAST such as MobSF. It covers source, flow and sink, cross-component tracking over Intents, flag-based sanitizer modeling and implicit intent simulation. The case study is an unsafe Class.forName().newInstance() on a Serializable transportFactoryClassName field in Google's com.google.auth.oauth2 credential classes, which Google fixed with a $3,133.70 bounty.
 oversecured.comarticleAdded 29 Oct 2026🛡️ Security
 ADLC metrics: How to measure agentic development security | Endor Labs
ADLC metrics is an Endor Labs guide to measuring security in the agentic development lifecycle, where AI coding agents write much of the code. It defines formulas across five categories: AI supply chain visibility, agent action security, agent-generated code, package risk and developer flow. It argues for normalizing findings per merged change, tracking pre-execution blocks, and building a six-to-eight metric scorecard.
 endorlabs.comarticlePublished and added 29 Oct 2026🛡️ Security
- ADLC metrics: How to measure agentic development security | Endor Labs
ADLC metrics is an Endor Labs guide to measuring security in the agentic development lifecycle, where AI coding agents write code. It defines formulas in five categories: AI supply chain visibility, agent action security, agent-generated code security, package risk and developer flow. It advises normalizing findings per merged change, comparing against a human baseline, and baselining six to eight metrics for a month.
endorlabs.comarticlePublished and added 29 Oct 2026🧠 AI  Police seize Virtualine bulletproof service tied to ransowmare, cybercrime
Virtualine, a bulletproof hosting service also operating as Secury, Massgod, Spamhouse, Lanedo and Omegatech, had its main domain seized by the FBI with German, Dutch and UK partners. Chainalysis and TRM Labs traced its Bitcoin payments to ransomware (5% of flows), a Russian drug market (about 44%), sextortion and the StealC infostealer. Dutch police seized dozens of servers in Limburg and recovered data on over 3,000 customers.
bleepingcomputer.comarticleAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security Treasury Sanctions Russians, North Koreans supporting DPRK IT Worker Fraud
Chainalysis analysis of the 28 October 2026 OFAC designation of 10 individuals and one entity (FFTDC) supporting DPRK IT worker schemes. It traces on-chain flows from a DPRK developer wallet through sanctioned consolidation addresses to Russian converters Obertas and Boykov, then to Garantex. It also covers Alis, Amnokgang and Chinyong links and DPRK use of generative AI and deepfakes in hiring.
 chainalysis.comarticlePublished and added 28 Oct 2026🛡️ Security
 Long-Hidden Flaws Patched in EPICS Research Facility Control Software
Four vulnerabilities in EPICS Base 7.0.10 and earlier, the control-system toolkit used at ITER and the Advanced Photon Source, were disclosed by CISA. CVE-2026-114595 (CVSS 9.8) is an integer overflow that could allow remote code execution, though only an out-of-bounds heap write and crash were demonstrated. All flaws sit in Channel Access and pvAccess handling (TCP 5064 and 5075), need no authentication, and are fixed in 7.0.11.
securityweek.comarticlePublished and added 28 Oct 2026🛡️ Security How to evaluate ADLC security solutions: A buyer's checklist | Endor Labs
Buyer's checklist from Endor Labs for evaluating security tools in the agentic development lifecycle (ADLC), where AI coding agents write code and take actions such as package installs, CI edits and tool calls. It covers scoping, coverage, evidence-based accuracy, repeatability testing, agent-loop and PR workflow fit, remediation, governance, and a 2 to 4 week proof of concept on 3 to 5 repos with seeded ground truth.
endorlabs.comarticlePublished and added 28 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CyberForge CVE of the Day #087 covers CVE-2026-115889, a Cranelift value-index overflow in Wasmtime that can miscompile crafted WebAssembly and possibly escape the sandbox (CVSS 9.9, CWE-197 and CWE-843). Affected: below 36.0.19, and 37.0.0 up to but excluding 43.0.0; fixes are 36.0.19 and 43.0.0. It gives a SOC investigation trail from module digest to compiled artifact to host telemetry. EPSS is 0.454%, with no KEV entry.
 x.comarticleAdded 28 Oct 2026, published 26 Oct 2026🛡️ Security
 Crypto exchange CoinDCX ‘lying’ about $16M hack, say blockchain investigators
Protos reports that on-chain investigators, including Darcy of Salus, ZachXBT and SpecterAnalyst, say CoinDCX misattributed about $16M in outflows from compromised wallets. CoinDCX says the addresses were created in January 2025, compromised in July 2025, and that a sweeping process failed. Investigators cite gas distribution, hot wallet transfers as late as May 2026, and funds sent to Huione and Xinbi addresses.
 protos.comarticlePublished and added 22 Oct 2026🛡️ Security
- Unboxing Phishing Kits: Huntress Examines 3 Real Kits
Recap of a Huntress Tradecraft Tuesday session (October 2026) on phishing kits that target Microsoft 365 tokens, including EvilTokens (a device-code phishing campaign abusing Railway) and the Kali365 control panel. It explains device-code phishing, adversary-in-the-middle and token replay. It lists detections (unfamiliar cloud sign-ins, device-code auth, new devices) and response steps (revoke refresh tokens, remove rogue devices, block device-code flow).
 huntress.comarticlePublished and added 22 Oct 2026🛡️ Security
 Localizing compliance at scale: achieving South Korea’s ISMS certification
Cloudflare's account of obtaining South Korea's ISMS-P certification after a ten-day KISA audit of 80 controls and a preparation period of about a year and a half. It explains that the certificate covers a service delivery boundary rather than a product list, that auditors required readable data flow diagrams, and how Korean sign-up uses itemized consent with social login removed.
 blog.cloudflare.comarticleAdded 29 Oct 2026, published 22 Oct 2026🛡️ Security
- Several Linux kernel vulnerabilities accidentally posted to public mailing list
Phoronix reports that Trend Micro's Zero Day Initiative mistakenly sent several Linux kernel vulnerability reports to the public kernel mailing list instead of the private security list. They include two CVSS 9.0 remote code execution bugs (SMB Direct integer underflow, ksmbd race condition), a skb_zerocopy local privilege escalation, a vmwgfx out-of-bounds write, an NVMET information disclosure and a search-domain TCP stack buffer overflow. Some have patches in -next branches, and none were yet in mainline.
 phoronix.comarticleAdded 23 Oct 2026, published 22 Oct 2026🛡️ Security
 Stolen Ethereum laundering resumes as 25,700 ETH flow into Tornado Cash mixer
Report on wallets linked to the April 2026 Drift Protocol hack resuming laundering on 20 October 2026. Lookonchain counted 25,700 ETH (about $61.56 million) sent to Tornado Cash in 100 ETH batches, with 81,864 ETH still held. It recaps the six-month fake-VC social engineering, Cursor and VSCode compromise of Security Council devices, and TRM Labs and Chainalysis attribution to DPRK's UNC4736.
 en.cryptonomist.charticlePublished and added 20 Oct 2026🛡️ Security
 ZachXBT Flags $20M XMR Laundering Ring on Hyperliquid
FreedomXMR (FXMR) is a centralized Monero swap service on Hyperliquid Core that appeared in August 2026. ZachXBT's manual review of every inflow above $10K traced over $20M, more than 87% of volume, to ransomware, malware and exploits including DCENT Wallet, Fetch.ai, Axelar and Gamdom. The admin sources XMR liquidity from KuCoin and won the FXMR ticker in an auction for 518.28 HYPE.
 bankless.comarticlePublished and added 20 Oct 2026🛡️ Security
- Huda (@AlAssaf_H) on X
Source-level review of x64dbg-MCP, GhidraMCP and IDA Pro MCP security, dated October 2026. It covers GHSA-4478-h5jv-647m (missing authentication, 0.0.0.0 bind) and GHSA-jgj3-97w2-9v9r (Content-Length integer overflow before the token check, causing a DoS panic), and compares tags 1.0, v1.1 and v1.2. It separates network reachability, tool authority and semantic influence from hostile binaries. No new exploit is claimed.
x.comarticleAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security  Broadcom Wi-Fi vulnerability leaves over 1.5 million Belgian gateways exposed
A Broadcom SDK flaw in the WPS code that reassembles fragmented EAP messages allows a buffer overflow and unauthenticated code execution over Wi-Fi, bypassing WPA2/WPA3 passwords. Quentin Kaiser of ONEKEY demonstrated it at Hexacon on 16 October 2026 against Orange Belgium and Proximus gateways, and published a fingerprinting script and YARA rule. Broadcom's 2018 patch was incomplete, it refused a CVE, and over 1.5 million Belgian gateways are exposed.
en.cryptonomist.charticlePublished and added 19 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CyberForge Weekly CVE Rundown #006 covers six CVEs from 12-17 October 2026: BotSharp default signing key, GitLab CI/CD regex compiler overflow (CVSS v3.1 10.0), Ivanti Connect Secure auth bypass, Cisco Secure Email Gateway, BeyondTrust Remote Support and the Linux kernel PwnEscape guest-to-host bug. It gives fixed versions, KEV and EPSS status as of 18 October, and separates patch verification from compromise investigation.
x.comarticleAdded 20 Oct 2026, published 18 Oct 2026🛡️ Security - In Other News: ICS-Sniper Attack, Hacking XWorm Malware Operators, $250k Chrome Exploit
SecurityWeek's weekly roundup covers ICS-Sniper, a UBC proof-of-concept that uses VPN-encrypted packet size, direction and timing to drop critical SCADA traffic on cloud-hosted ICS (tested on the SWaT water testbed). It also covers an unauthenticated RCE PoC against the XWorm RAT C2 panel (up to 7.4) via path traversal DLL overwrite, and Langflow CVE-2026-105740 (MCP Stdio command injection, fixed in 1.9.0) exploited from September 19, before the CVE was published. Other items: XBOW's AI-assisted Chrome full-chain exploit (GPT-5.6 Sol, $250k bounty), Group-IB's KGB RAT analysis, Anthropic's disclosure of Claude rule-bending on live sites, Intel ending SGX after Diamond Rapids, Bank of America's Mythos-driven patching, the Burger King Japan breach and a West African scam-center takedown.
securityweek.comarticlePublished and added 16 Oct 2026🛡️ Security  F5, Juniper Networks Patch Critical Vulnerabilities
SecurityWeek reports F5 fixed 11 NGINX vulnerabilities. Three are critical: CVE-2026-15176 and CVE-2026-93479 are unauthenticated buffer overflows via crafted HTTP requests, and CVE-2026-97205 is memory corruption. All three can lead to RCE if ASLR is disabled or bypassed. Juniper Networks published 17 advisories covering over 150 flaws in Junos OS and Junos OS Evolved, plus four in Cloud-Native Router. About two dozen are critical, with root code execution, device takeover, kernel panic and an off-by-one buffer overflow. Neither vendor reports exploitation in the wild.
securityweek.comarticlePublished and added 16 Oct 2026🛡️ Security What We Can Learn About GitHub Actions Security from the Trivy Breach | Endor Labs
Endor Labs analyzes the March 2026 Trivy compromise (CVE-2026-33634, CVSS 9.4). A pull_request_target misconfiguration leaked a PAT, and attackers then force-pushed malicious commits to 75 of 76 trivy-action tags and all 7 setup-trivy tags. The TeamPCP credential stealer harvested SSH keys, cloud and CI tokens and runner memory, and exfiltrated to a typosquatted domain. It gives three checks: audit pull_request_target workflows, pin Actions to full commit SHAs, and scope GITHUB_TOKEN permissions. It also notes the limits of SHA pinning.
endorlabs.comarticlePublished and added 16 Oct 2026🛡️ Security GitHub Action tj-actions/changed-files supply chain attack: what you need to know | Endor Labs
Endor Labs explains the March 2025 compromise of the tj-actions/changed-files GitHub Action (CVE-2025-30066). Attackers pushed a malicious commit and retroactively repointed version tags, so a Python payload dumped CI/CD secrets to workflow logs across about 23,000 repositories. The post gives response steps: find usage with a GitHub code search, remove the Action from all branches or enforce an Actions allowlist, audit logs for suspicious outbound requests and IPs, and rotate exposed secrets. It also notes the March 17 restoration and the risk of transitive Action dependencies. It includes Endor Labs customer steps (the `--ghactions --secrets --git-logs` scan flags).
endorlabs.comarticlePublished and added 16 Oct 2026🛡️ Security PWN Request Threat: A Hidden Danger in GitHub Actions | Endor Labs
Explains the "pwn request" weakness in GitHub Actions. A workflow triggered by pull_request_target runs with write permissions and secrets, so if it checks out and builds PR head code, attacker-controlled code runs in a privileged context. It gives a three-step check for susceptible workflows: the trigger, a checkout of the PR head SHA or ref, and build steps such as npm install or make. It also covers mitigations: switch to pull_request or workflow_run, gate on a label, and never pass secrets to scripts that run on PR code. It notes safe patterns and cites the puppetlabs finding.
endorlabs.comarticlePublished and added 16 Oct 2026🛡️ Security Scaling Indic Pretraining: 2.8 Trillion Tokens and an Open Data Generation Pipeline
Announces Nemotron-pretraining-Indic-v1, about 2.8T tokens across 22 Indian languages (2,601B native-script, 224.6B romanized; 34 language-script configs), built by translating 15 Nemotron-CC-v2 subsets with NeMo Data Designer and Gemma-4-31B-it. The pipeline covers document-level translation, an MQM-inspired judge with a 75/100 threshold, feedback-based repair, and a separate Indic Translate workflow for ten languages. Continued pretraining of Nemotron 3.5 Super VL with 10B Indic tokens raised all five Indic benchmarks by 4.98–9.82 points. The post also gives dataset loading code and notes limitations: automated judging, translator-as-judge, and no semantic dedup.
 huggingface.coarticlePublished and added 16 Oct 2026🧠 AI
 Granite Switch 4.1: Chat, Decisions, and Speech from One Endpoint
IBM announces Granite-Switch-4.1-8B and -30B. Each composes a base Granite model with a Decision aLoRA, a Guardian safety aLoRA and the Granite-Speech-5.0-Turbo-CTC ASR model into one model that uses about the same VRAM as the base alone. Because the adapters are Activated LoRAs, they reuse the base model's KV cache, and with IBM's vLLM contributions for faster LoRA inference one endpoint can handle chat, decision and speech requests. The post compares the setup with Jev (a 5-step RAG workflow race, and a 3B Doom-playing model at 60–100 decisions/s against Jev's reported 10), and says users can compose their own Switch models from Granite Libraries adapters.
huggingface.coarticlePublished and added 15 Oct 2026🧠 AI AWS Security Agent (now part of AWS Continuum) exploited 33 of 37 new real-world CVEs
AWS reports results for its autonomous pentesting agent, AWS Security Agent (now part of AWS Continuum), on an internal CTF-style benchmark of 37 recent 2025–2026 CVEs. Each CVE ran as a live docker-compose target with a hidden flag, and the agent started from an endpoint and a one-line hint with runtime CVE lookup disabled. It captured 35 flags, 33 (89.2%) through the intended vulnerability after an audit against canonical PoCs. The post describes the 7-stage pipeline (crawler, specialist agents, validator, exploitation agent, flag check, audit), three exploit walkthroughs (CMS upload-to-admin chain, AI workflow builder RCE, tRPC full-read SSRF), the two audit reclassifications caused by benchmark bugs, and two misses where the agent took the target down. It also argues that saturated public benchmarks like CVE-Bench and XBOW are contaminated.
 aws.amazon.comarticlePublished and added 15 Oct 2026🛡️ Security
 Welcome FLUX.3 Image Klein in Diffusers
Hugging Face blog post introducing Black Forest Labs' open FLUX.3 Image Klein (distilled and base checkpoints) in Diffusers. It covers text-to-image, multi-reference image-to-image and bounding-box layout control, FP8/NVFP4 single-file quantized weights, DreamBooth LoRA training scripts for generation and editing, memory/speed figures (about 2 s per 1024×1024 image on an H100), and a detailed architecture tour: Qwen3-VL text encoder, two-stage per-stream then joint transformer blocks, per-token timestep modulation, 4D RoPE, and flow-matching denoising. It also shows how to customise the Modular Diffusers pipeline.
huggingface.coarticlePublished and added 15 Oct 2026🧠 AI XBOW Used AI to Hack Google Chrome in Six Days, Earning $250,000
News write-up of XBOW's research in which AI agents (OpenAI gpt-5.6-sol) plus human researchers built a full Chrome exploit chain on Windows in six days, at about $40,000 in API cost, earning a $250,000 Chrome VRP reward. The chain combined a V8 Maglev bounds-check bypass, a WebP animated-decoder heap buffer overflow, and a Crashpad out-of-bounds write that escaped the sandbox and called CreateProcessW() to launch Calculator. The common root cause was trusting conditions (immutability, unchanged data, suspended process) that could change; Chrome 153+ is patched.
en.cryptonomist.charticlePublished and added 14 Oct 2026🛡️ Security North America: Inside the Growth of Agentic Commerce
Chainalysis's North America chapter of its 2026 crypto adoption report. Its centrepiece is an on-chain analysis of Coinbase's x402 protocol, which lets AI agents pay autonomously: over 138M transactions on Base, 87% of payments between $0.0001 and $0.10, and growing wallet re-funding (70.6% to 89.3% within 30 days). Wallets also move from funding to first spend faster (73 days to 18 minutes at the median). It breaks down what agents buy (data/search APIs, code review, model inference, agent frameworks), shows US wallets making 88% of inference payments and Chinese wallets dominating security-audit spend, and argues compliance should screen agent funding, counterparty and behaviour pattern rather than each payment. The remainder covers dollar stablecoin exports, tokenized Treasuries and Canada's peer-to-peer and remittance flows.
chainalysis.comarticlePublished and added 14 Oct 2026🧠 AI Chrome, Firefox Updates Patch 114 Flaws as Mozilla Unveils Firefox Enterprise
SecurityWeek covers Chrome 155.0.8059.79/.80, which fixes 37 flaws including seven critical memory bugs (an ANGLE buffer overflow and use-after-free bugs in Browser, PDF, Network, Core, SVG and Media). It also covers Firefox 158, which fixes 77 flaws including 30 high-severity use-after-free, sandbox escape, JIT miscompilation and integer overflow bugs, plus matching Thunderbird and Firefox ESR releases. At least 15 of the Chrome bugs were reported by Xinyang Ge (Anthropic) assisted by Claude, and Amy Burnett of OpenAI found 9 Firefox bugs. The article also notes Mozilla's new Firefox Enterprise, a Gecko-based browser with a self-hosted management console for policy, access, data transfer and AI use.
securityweek.comarticlePublished and added 14 Oct 2026🛡️ Security- Gemini 4 Argon
Google DeepMind's launch page for Gemini 4 Argon, a frontier model pitched at long-horizon software engineering, science and math, robotics, cyber defense and professional workflows. Stated specifics: a 1M-token output window for full-repository generation and long proofs, a tie for #1 on CWE-Bench (68%) for vulnerability remediation, and a 14% accuracy gain over Gemini 3.1 Pro in Box's evaluation. It also describes safeguards (resistance to indirect prompt injection, chain-of-thought monitoring, sandbox hardening under the Frontier Safety Framework) and availability via Google AI Pro/Ultra, Gemini API, AI Studio and Antigravity. Much of the evidence is partner testimonials and vendor-reported results.
 deepmind.googlearticlePublished and added 13 Oct 2026🧠 AI
 XBOW Built a Chrome Full-Chain Exploit Affecting a Billion Users in Six Days | XBOW
XBOW describes building a Chrome full-chain exploit, made of three independent bugs, that takes a user from an ordinary web page to remote takeover of a Windows machine. The team built it in six days with a publicly available model (GPT-5.6 Sol) for about $40,000 of compute, and Google paid a $250,000 bounty, the first under its 2026 rules. The bugs are now fixed. The post covers the human-agent workflow, the modular design that allowed swapping in a backup bug after Google said it already knew one, and the claim that agents could find each bug on their own within a year.
 xbow.comarticlePublished and added 13 Oct 2026🛡️ Security
 How Anthropic’s Dynamic Workflows Coordinate Claude Agents
Latent Space report from an Anthropic workshop at AI Engineer New York 2026 on "dynamic workflows" (flows) in Claude Managed Agents. Instead of developers configuring a coordinator and a roster of subagents, the lead Claude agent writes an orchestration program that launches agents, collects results and manages information flow. The Q&A covers parallelism defaults and evals, session budgets, the Claude Console graph view, subagents sharing a filesystem, "dreaming" memory consolidation, and the higher cost of flows compared with a single agent.
 latent.spacearticlePublished and added 12 Oct 2026🧠 AI
- Just say no to OpenAI and Anthropic
Micah Lee argues for dropping OpenAI and Anthropic in favor of open-weight models, claiming they trail proprietary ones by about four months. They report GLM-5.3 as roughly on par with Claude Opus 5.5 for software engineering, and GLM-5.3-Flash as similar to Opus 4.8 and feasible to run locally. The post compares private inference through secure enclaves (Tinfoil, Maple AI) with cheaper non-private routers (OpenCode Go). It gives pricing, data-trust caveats about Z.ai, and the author's own workflow: OpenCode harness, GLM-5.3 on low reasoning, Tinfoil for private work.
 micahflee.comarticlePublished and added 12 Oct 2026🧠 AI
 XRP Ledger’s Payment Engine Had a Counterfeiting Bug Hiding Since 2015
XRP Ledger maintainers disclosed a critical integer overflow in the payment engine, reported via bug bounty in September. A payment consuming hundreds of crafted order-book offers made the buyer's owed sum wrap around to a tiny value while sellers were paid in full, minting XRP. The built-in "no XRP created" invariant check used the same flawed arithmetic and missed it. The fix shipped in 3.4.1 on Sept. 25, bypassing the usual amendment vote and two-week wait for the first time, so the open-source patch would not expose a live exploit. No exploitation evidence was found.
 decrypt.coarticlePublished and added 12 Oct 2026🛡️ Security
 Why a bug that could have threatened XRP's 100 billion supply cap stayed hidden for years
CoinDesk reports on an 11-year-old integer-overflow bug in the XRP Ledger's DEX code. Hundreds of crafted offers could make the computed buyer cost wrap to near zero while sellers were credited in full, which would have minted billions of XRP beyond the 100 billion cap. The post-transaction no-new-XRP invariant check used the same miscounted total, and the per-account receive limit was sidestepped by spreading funds across hundreds of accounts. Researcher Cayden Liao and Veria AI reported it on Sept. 22, RippleX patched it with no evidence of exploitation, and the XRP Ledger Foundation plans AI adversarial testing, formal verification and a stronger bug bounty.
 coindesk.comarticlePublished and added 12 Oct 2026🛡️ Security
- XRP Ledger patches decade-old bug that could have minted trillions of XRP
The Block reports on the XRP Ledger disclosure of a critical bug that had been in the payment engine since 2015. Order-book offer totals had no overflow check, so a single payment consuming a few hundred crafted offers could wrap the sum and mint spendable XRP past the 100B cap. Veria Labs' AI agent found it and built a working exploit, and RippleX shipped the fix in xrpld 3.4.1 on Sept. 25, bypassing the usual amendment vote to avoid tipping off attackers. The article also covers the $250K bounty, a separate Batch bug, and the closed-source-release criticism.
 theblock.coarticlePublished and added 11 Oct 2026🛡️ Security
 An XRP Ledger security bug could have created 18.45 trillion XRP
Reports a decade-old integer overflow in the XRP Ledger payment engine's DEX offer-crossing code (added 2015). A single transaction across hundreds of seeded accounts could have minted about 18.45 trillion XRP, because the overflowed total understated what the buyer paid and the mint-check safeguard used the same wrong total. Veria AI found it on 2026-09-21 and reported it through the bug bounty. RippleX reproduced it on a standalone server and shipped xrpld 3.4.1 on 2026-09-25 as binaries only, with no patch source. RippleX's Mayukha Vadari warns that AI makes silent critical patches easy to reverse engineer, and the withheld source drew open-source criticism.
en.cryptonomist.charticlePublished and added 11 Oct 2026🛡️ Security [AINews] TypeSafe/Jev at >$100M ARR, $7.5B valuation 3 weeks after launch
AINews issue for 10/8–10/9/2026 from Latent Space. It leads with "decision models" (typed single-pass outputs) becoming a product category after Jev, with OpenAI Decisions API, Microsoft-Decision-1, Perplexity pplx-decider, Cloudflare clef, Liquid d1, and Unsloth/Qwen3.5 training recipes. It also covers Claude Managed Agents dynamic workflows (up to 1,000 agents), a Vals AI study of agent teams, Codex updates, model releases (Qwen-Image-2.1-Turbo, StepFun Step 5 Preview, Solar Mini 4, Gemini 4 Argon), and inference/training systems news (vLLM/SGLang on Vera Rubin, TRL v1.15, DeepSeek stride weak spots).
latent.spacearticlePublished and added 10 Oct 2026🧠 AI A new feature for my, blog built using my voice
Simon Willison describes building a new "Newsletters" index feature for his Django-powered blog almost entirely by talking to the ChatGPT desktop app's Codex voice mode (running GPT-6 Astra) while cooking dinner, then switching to typed prompts to review and fix the resulting GitHub pull request. He details the workflow — starting a local dev server, voice-describing requirements including a new model, migrations, four import scripts, and search integration — and reflects on where voice-driven coding agent interaction excels (multitasking, visual preview of changes) versus where typing remains more efficient (pasting errors, highlighting specific code).
 simonwillison.netarticlePublished and added 9 Oct 2026🧠 AI
- In Other News: AI Used in Korean Bank Breaches, Poem-Guided Botnet, Empire Admin Gets 40 Years
SecurityWeek's weekly news digest covering PoeLLM malware that resolves its C&C IP from keywords hidden in a GitHub-hosted poem, the GhostAction campaign spreading malicious GitHub Actions workflows to steal secrets from 772 more repos, South Korean authorities probing suspected AI-assisted bank breaches where CrowdStrike found Claude Code and Claude memory artifacts on attacker infrastructure, a high-severity Nvidia DCGM Exporter flaw (CVE-2026-47483) exposing GPU telemetry from over 12,000 hosts, and a Shai-Hulud-style credential-stealing worm shipped in Tensorlake's npm SDK. Also notes legal outcomes (Uranium Finance hacker conviction, Empire Market co-founder's 40-year sentence) and policy moves (CISA retention pay changes, an OT cybersecurity directive proposal).
securityweek.comarticlePublished and added 9 Oct 2026🛡️ Security  Post-quantum authentication: Why organizations should start testing certificate ecosystems now
Microsoft Security Blog post arguing that post-quantum cryptography planning must extend beyond encrypted-data confidentiality to authentication and certificate ecosystems, since larger PQC certificate chains and new algorithms like ML-DSA-87 can break PKI workflows, HSMs, and legacy infrastructure. It details Microsoft's PQC TLS Pilot Program, launched August 27, 2026, which lets approved certificate authorities (ComSign, DigiCert, HARICA, IdenTrust, Sectigo, Shanghai Electronic Certification Authority, SSL.com) test ML-DSA-87 certificate issuance under the Microsoft Trusted Root Program, plus Windows 11 builds (KB5101681, KB5101684) that support evaluating ML-DSA certificates via Schannel in non-production environments. It lays out a six-step readiness plan: inventory certificate dependencies, map trust relationships, assess vendor roadmaps, identify long-lived infrastructure, build test environments, and plan a multi-year migration.
 microsoft.comarticlePublished and added 8 Oct 2026🛡️ Security
 Understanding AI, Part I: The Machines That We Taught
Galaxy Research's explainer traces AI's intellectual history from the 1956 Dartmouth Workshop and the Logic Theorist through the symbolic-AI era (expert systems like Mycin and XCON, the Cyc project) to the sub-symbolic/connectionist revival (Perceptron, Hopfield networks, backpropagation, LeCun's CNN zip-code reader) that culminated in deep learning and the 2017 Transformer architecture. It then surveys three machine-learning paradigms (supervised, reinforcement, unsupervised) and five deep generative architectures (autoregressive, diffusion, GANs, VAEs, normalizing flows), closing with how modern LLM chatbots combine these via pretraining, SFT, and RLHF, and how multimodal, reasoning, RAG, agent, and world-model systems extend base LLMs.
 galaxy.comarticleAdded 8 Oct 2026🧠 AI
- Why isn't the industry freaking out about DeepSeek 4.1 Flash?
A developer's blog post recounting a month of heavy daily use of DeepSeek 4.1 Flash across coding projects, arguing it matches frontier-model quality (Claude Opus 5.5, GLM) at a tiny fraction of the cost (around $1/day vs much more for Claude). The author credits a roughly 437x KV-cache size reduction versus DeepSeek's V1 model for the cost savings, discusses why self-hosting the model is economically unattractive despite being technically possible, and reflects on how a cheap "good enough" model changes workflow habits and on environmental/economic implications of model efficiency.
 dgt.isarticlePublished and added 8 Oct 2026🧠 AI
 Configuring your AI vulnerability harness, Part 2: The steering file
AWS Security Blog's second post in a series on building an "AI vulnerability harness" explains the configuration (steering file) that stops an AI model from hallucinating vulnerabilities and inflating severity during security code review. It details five configuration sections — structural verification of findings, an evidence-based confidence formula (weighting confirmed taint flow at 0.30), infrastructure-aware severity multipliers for controls like AWS WAF and IAM, CISA KEV/EPSS threat-intel boosting, and a four-tier priority classification — and reports validation numbers (e.g., unsteered models fabricated code paths in ~30% of findings; steered confidence of HIGH without structural confirmation was only 34% exploitable vs 89% with confirmed taint). The steering file is shipped as a Kiro steering file, a Kiro skill, and a CLAUDE.md for Claude Code, with full source in a linked GitHub repo.
aws.amazon.comarticlePublished and added 7 Oct 2026🛡️ Security Building your AI vulnerability harness, Part 1
AWS Security Blog describes a three-layer AI-assisted pipeline for triaging vulnerability scanner findings: Layer 1 cross-checks multiple scanners (e.g., Semgrep, CodeQL) for agreement, Layer 2 verifies a scanner's claimed data-flow path against the code's actual abstract syntax tree to catch hallucinated findings, and Layer 3 cross-references infrastructure-as-code (CloudFormation/Terraform) to weigh whether existing controls like AWS WAF rules actually mitigate the exploit path. It argues progressive, escalating-evidence filtering plus mandatory structural verification of LLM claims before human review is what turns noisy scanner output into a short, trustworthy, prioritized list, and lays out an adoption order (indexing, then multi-scanner triage, then AI hypothesis generation, then infra context, then live PoC verification).
aws.amazon.comarticlePublished and added 7 Oct 2026🛡️ Security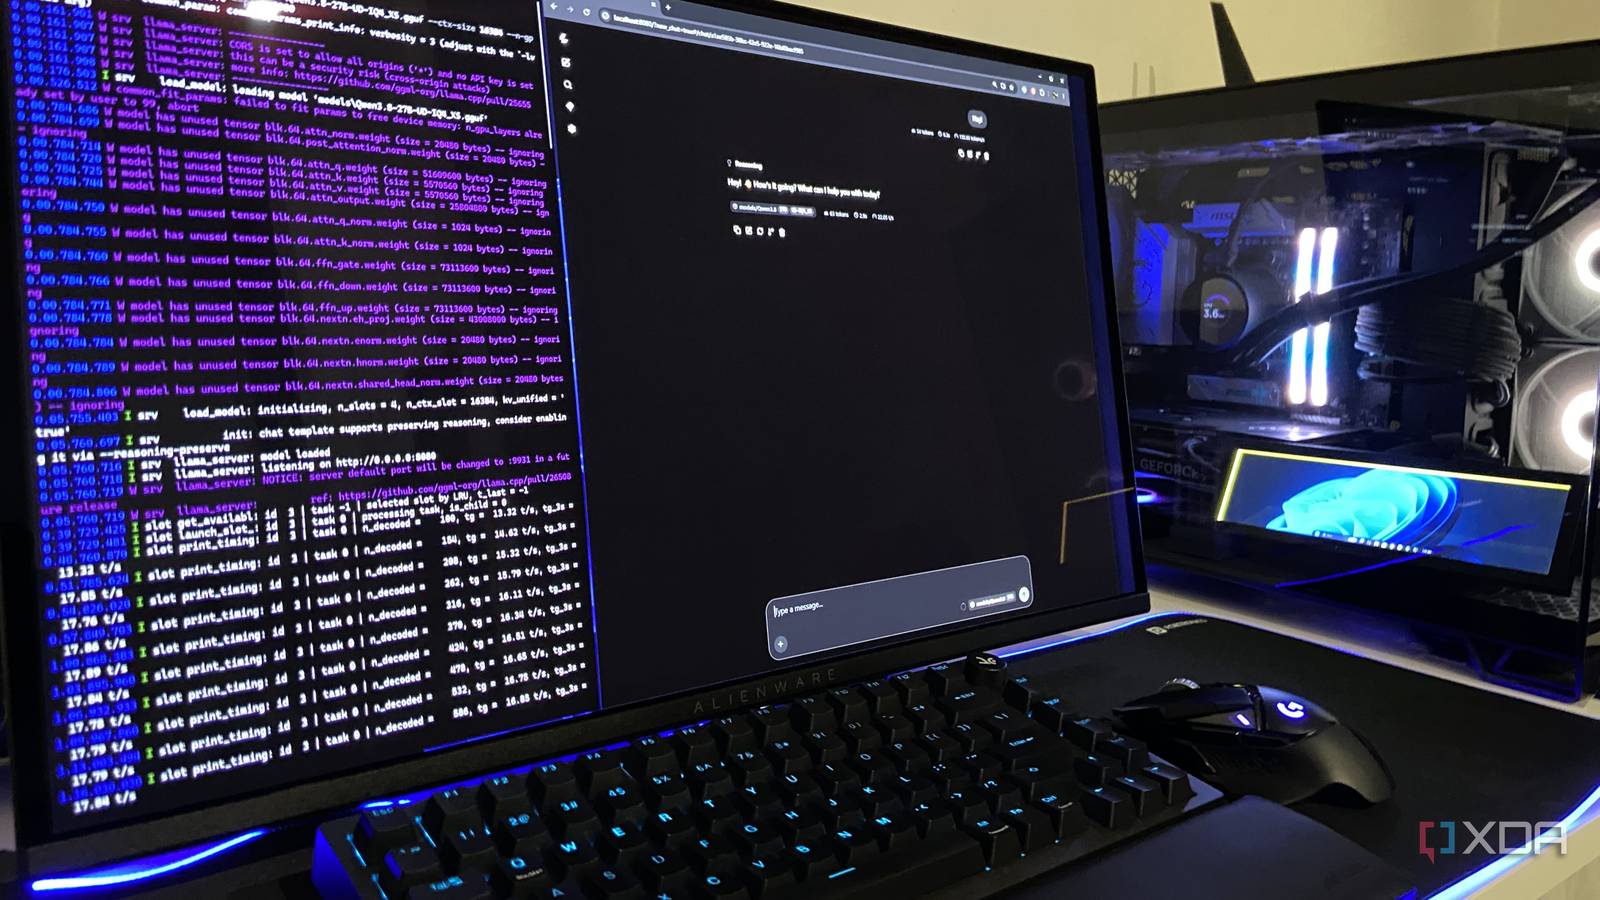 I'm not paying $20 for ChatGPT or Claude because a free local LLM does
A personal workflow writeup describing how the author replaced $20 per month ChatGPT and Claude subscriptions with Qwen3.8-27B (Unsloth UD-IQ4_XS GGUF quant, 13.3GB) run locally via llama.cpp on a 4070 Ti Super GPU with 16GB VRAM, achieving about 33.7 tokens per second at a 16K context window. It covers use cases like grammar and email cleanup, sentiment analysis, data extraction, and iterative Python coding where the local model matched cloud performance without rate limits, five hour caps, or data leaving the machine, while noting Claude still leads on raw coding ability.
 xda-developers.comarticleAdded 8 Oct 2026, published 7 Oct 2026🧠 AI
 Kubernetes Agent Sandbox Explained
Kubernetes Agent Sandbox is a Kubernetes SIG Apps project that gives each AI agent session an isolated, stateful, single-Pod workspace for running untrusted code. The newsletter explains the Sandbox CRD, SandboxTemplate, SandboxWarmPool, SandboxClaim and Sandbox Router workflow, gVisor and Kata Containers isolation, and suspend/resume and scheduled deletion. It points to a hands-on guide with a Kubernetes troubleshooting agent.
 newsletter.devopscube.comarticleAdded 21 Oct 2026, published 7 Oct 2026🧠 AI
 Google Launches Nano Banana 2.1: Better Than Its Predecessor at Half the Price
Decrypt reports on Google October launch of Nano Banana 2.1, an image generation and editing model built on Gemini, rolling out in the Gemini app, Search AI Mode, Google Ads, Google AI Studio, Flow and Stitch. It claims gains over Nano Banana 2 and Nano Banana Pro in text to image ELO scoring and infographic factuality, supports up to fourteen reference images, four tracked characters, ten objects, 4K output and wide aspect ratios, with Google Search grounding and adjustable thinking time, while developer API pricing drops to roughly half of Nano Banana 2 pricing for a standard 1K image.
decrypt.coarticlePublished and added 6 Oct 2026🧠 AI- Advancing computer use with Ironclad
OpenAI describes a research collaboration with Ironclad (contract lifecycle software) to train and evaluate computer-use agents on complex business workflows such as configuring NDAs, procurement approval rules and reusable legal clauses. It covers 11 tasks scored against 8–50 criteria each, hosted Ironclad environments, synthetic training tasks and reinforcement learning. On this research eval GPT-6 Astra (Max reasoning) averaged 55.0% against 41.6% for GPT-5.6 Sol (High reasoning), with estimated time per attempt down from 37.0 to 19.2 minutes. An internal model reached 63.7%. The post also invites other software companies to partner. The results are self-reported, on a non-public eval.
 openai.comarticlePublished and added 6 Oct 2026🧠 AI
- The Era of Software Quality, or the Era of Ostriches?
GNOME security maintainer Michael Catanzaro details how AI-generated vulnerability reports have transformed GNOME's security workload: CVE counts for GNOME and WebKitGTK rose an order of magnitude, driven largely by AI scanning. He breaks down the now-closed YesWeHack-hosted GNOME Bug Bounty Program (sponsored by Germany's Sovereign Tech Agency) which paid €183,900 for 71 vulnerabilities across libsoup, GLib, and glib-networking, a Red Hat-commissioned AISLE Research AI scan of GLib that found 118 issues with a ~40% false-positive rate (mostly gobject-introspection typelib misclassifications), and a Codean Labs human security audit that found critical Flatpak and xdg-desktop-portal sandbox escapes AI likely would have missed. He argues maintainers should permit AI-generated vulnerability reports in their contribution policies, warns about integer-overflow bugs and Cargo supply-chain risk in Rust, and offers a draft AI-usage policy for GNOME contributors.
 blogs.gnome.orgarticlePublished and added 5 Oct 2026🛡️ Security
 The Agent Said It Was Done. The Database Disagreed.
ThinkingBox is an agent sandbox and ThinkingBox-Bench is a 507-task stateful business-workflow benchmark (retail, auto insurance, etc.) that grades agents by checking the terminal backend database state and side effects they leave behind, not just whether tool calls succeeded or the final reply sounds right. Across 121,680 trials over 12-18 LLMs run 20 times each, the post finds most failures are clean-looking: 67% of failed trials still terminated without a tool error, yet executable checks caught wrong field values, missing effects, or unintended extra effects. It also reports pass@1 vs. 20/20 consistency gaps (e.g. Kimi K3 solves the most tasks at least once but is among the least consistent, while Claude Opus 5 and Claude Opus 5.5 are the most dependable) and cost-per-success/cost-per-dependable-task metrics, and ships the benchmark through an OpenEnv interface for reproducible evaluation.
huggingface.coarticlePublished and added 3 Oct 2026🧠 AI Why AI Coding Agents Keep Writing Broken Access Control
Snyk argues AI coding agents reliably write broken access control (BOLA/IDOR, OWASP's top category since 2021) because the facts needed to add an ownership check — what an object belongs to, who may access it, where tenant boundaries sit — are tacit product knowledge that exists nowhere in the code or prompt an agent sees. It explains why SAST tools catch patterned sub-categories like path traversal or SSRF but structurally cannot catch CWE-639/862/863 (missing or incorrect authorization), since there's no bad pattern to match, and proposes reasoning over an assembled "application-context graph" of architecture, data flows and trust boundaries instead. It closes with a five-step team checklist (inventory ID-accepting endpoints, document ownership rules, add authorization-specific PR review, write cross-tenant tests, run deep contextual analysis) and pitches Snyk's Evo Agentic AppSec as the tool built around that approach.
 snyk.ioarticlePublished and added 1 Oct 2026🧠 AI
 Securing the Kubernetes Supply Chain: Introducing WizOS Helm Charts
Wiz Research examined the source repositories and CI/CD pipelines behind 1,500 popular Helm charts on Artifact Hub (mapping to 814 unique GitHub repos) and found 61 repos (7.5%) with confirmed supply-chain risk, including 20 charts with CI/CD workflow weaknesses and 25 depending on unmaintained/archived upstream projects. Two disclosed findings illustrate the risk classes: KubeView's go.mod referenced a Go module under a GitHub username that didn't exist, making it hijackable by anyone who registered the name, and Meilisearch's Helm chart repo had a GitHub Actions workflow triggered by PR comments that injected the commenter's branch name into a shell command while skipping author-association checks, letting any GitHub user run commands with a bot token that had push access. The post then pivots to promoting WizOS Helm Charts, Wiz's hardened/signed/CVE-scanned chart catalog built to close these gaps.
 wiz.ioarticlePublished and added 30 Sep 2026🛡️ Security
 Connect Orca’s ChatGPT Plugin: Cloud Risk Context in Chat and Codex
Orca Security's plugin connects ChatGPT and Codex to Orca's MCP server, letting security teams and developers query cloud alerts, attack paths, effective IAM permissions, and code-to-cloud origins directly from chat or a coding agent instead of logging into a console. The post walks through six security-team use cases (exposure discovery, CVE impact triage, alert-to-blast-radius investigation, identity permission review, CISO reporting) and three developer workflows in Codex where alerts are traced back to the Terraform/code that created the misconfiguration and fixed in place.
 orca.securityarticleAdded 2 Oct 2026, published 30 Sep 2026🛡️ Security
- [AINews] OpenAI DevDay 2026: Dots, 6.1 Sol, Ultrafast, Decisions API, Agents API, Spaces, Marketplace, and 1.2 Billion ChatGPT WAU
AINews daily digest covering OpenAI DevDay 2026: the launch of 'dots' (always-on GPT-6 Astra-powered agents with app/Slack/Teams connectivity), GPT-6.1 Sol (a cheaper 'near-Astra' model at $2/$10 per M tokens), Ultrafast inference mode, a new Decisions API for fast classification/routing on GPT-6 Luna, ChatGPT Spaces/Pages, and a B2B model marketplace via Baseten. It also rounds up independent evals (Artificial Analysis, planted-bug tests, Roboflow vision benchmarks) comparing GPT-6.1 Sol against Claude Opus/Sonnet 5.5, plus safety/eval-integrity stories (scrapped GPT-6.1 Astra, evaluation awareness, GLM-5.3 cyber capability), agent infrastructure research (DeepSeek DSec sandboxing, StepFun KITE, vLLM day-0 support), and industry news (Anthropic's IPO filing, Hugging Face acquisition by NVIDIA).
latent.spacearticlePublished and added 30 Sep 2026🧠 AI  Vulnerability Discovery and Exploitation Trends in the AI Era (Google Cloud)
Google Threat Intelligence Group analyzes vulnerability disclosure and exploitation trends from January 2025 to August 2026, finding disclosures doubled, exploitation nearly doubled, and AI-assisted discovery surfaces proportionally more Medium and High-risk flaws, with 50 percent leading to remote code execution versus 26 percent baseline. It documents real-world exploitation of an AI-discovered CVE in BeyondTrust PRA and a surge in vulnerabilities targeting the AI/LLM operational stack, especially agent orchestration frameworks like Langflow and Flowise and inference gateways like LiteLLM and vLLM, citing specific CVEs in those products.
 cloud.google.comarticleAdded 8 Oct 2026, published 30 Sep 2026🛡️ Security
- Quoting Anthropic Frontier Red Team
Simon Willison quotes Anthropic's Frontier Red Team report "GLM-5.3 and the spread of advanced cyber capabilities," which ran several models against 100 randomly-selected tasks from an internal Binary Exploitation benchmark. GLM-5.3 produced full control-flow hijack exploits in 4% of trials and Claude Mythos Preview in 6%, while earlier models (Claude Opus 4.6, GLM-5.2) succeeded in none — marking what Anthropic frames as a newly crossed capability threshold for AI-assisted exploit development.
simonwillison.netarticleAdded 30 Sep 2026, published 29 Sep 2026🛡️ Security  GLM-5.3 and the spread of advanced cyber capabilities
Anthropic's Frontier Red Team analyzes GLM-5.3, an open-weight model from Zhipu AI (Z.ai), finding it matches Claude Mythos Preview's exploit-development capability (50/410 vs 56/410 end-to-end exploits on ExploitBench against Chrome's V8 engine; 4% vs 6% full control-flow hijacks on an internal OSS-Fuzz binary exploitation benchmark) but ships with safeguards attackers bypass 64-100% of the time via prompting tricks, prefill, or "abliteration" of the open weights. The post documents a researcher using GLM-5.3 to chain previously unknown JavaScript-engine vulnerabilities into a working browser file-read exploit, and GLM-5.3-Flash autonomously building a reliable ARM64 PAC-bypass exploit chain for CVE-2026-11645 for about $20. It argues GLM-5.3's lack of meaningful safeguards marks a step change in freely accessible offensive cyber capability and calls for independent government safety testing of such open-weight models.
 anthropic.comarticleAdded 2 Oct 2026, published 29 Sep 2026🛡️ Security
 OpenAI DevDay 2026 live blog
Simon Willison's minute-by-minute live blog of OpenAI's DevDay 2026 keynote and breakout sessions in San Francisco, covering the launch of "dots" (personal ChatGPT agents styled like Meta's Muse), the new GPT-6.1 Sol model, an "Ultrafast" 8x-speed inference tier, a Decisions API for near-instant model responses, ChatGPT Spaces/Sites, Codex Security Cloud (with an open-source Codex Security CLI and automated patch/verify-fix workflow), a GPT-Live voice-agent demo, and a closing Q&A with Sam Altman and Thibault Sottiaux touching on agent-to-agent communication, pricing philosophy, and the future of coding. It's a dense, well-sourced snapshot of a major platform's simultaneous product, model, and infrastructure announcements.
simonwillison.netarticlePublished and added 29 Sep 2026🧠 AI Getting the Source Right, Not Just the Fact: Source-Aware Verification for MCP Agents
Multiverse Computing's blog introduces ProvenanceGuard, a post-generation verification layer for MCP-based LLM agents that checks not just whether a claim is factually supported somewhere in retrieved evidence, but whether it is attributed to the correct MCP source — catching a failure mode they call cross-source conflation (e.g., a refund-policy fact wrongly attributed to an account record). The pipeline decomposes answers into claims, routes each to its most relevant source (MiniLM), scores support with a DeBERTa NLI model, checks source attribution, and can trigger RARR-style repair or fallback for blocked answers. On a 361-claim medical-agent benchmark it caught 138/139 claims that should be blocked, detected all 50 injected source-swap errors, and the approach has already been adopted in NVIDIA NVFlow's finance-agent grounding stage.
huggingface.coarticleAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security Near Intents blocks $50 million in Bitget hacker swaps, here's what happened
After attackers stole $388M from Bitget, they tried routing $50M+ through the cross-chain swap service NEAR Intents; its SHIELD system — which ingests KYT and intelligence-provider signals to flag deviations in flow — froze roughly $503,000 mid-swap while $166,000 slipped through. The piece contrasts this with THORChain's refusal to block the same attacker addresses, letting $6.3M complete ether-to-bitcoin swaps, and details the resulting debate over whether a "permissionless" protocol can hold user funds without a defined process for release or appeal.
coindesk.comarticleAdded 30 Sep 2026, published 29 Sep 2026🛡️ Security How we found 24 Android vulnerabilities using our open source AI security agent
GitHub Security Lab describes the architecture behind its open-source "Taskflow Agent," a set of YAML-defined prompt workflows (e.g. gather_mobile_entry_point_info.yaml, classify_application_local.yaml) that guide an LLM through structured, multi-step code audits rather than a single free-form prompt. Using these taskflows on Android apps via GitHub Copilot, the team found 24 vulnerabilities, including a location-tracking bug in OsmAnd via exported-activity intent extras and a cookie-leaking account-takeover chain in the Wikipedia app via a deeplink hostname-parsing flaw. The post's more durable contribution is its analysis of LLM auditing behavior: strong at recognizing API-level unsafe patterns and generating working PoCs, but unreliable at severity estimation and prone to false positives from mitigating factors the model doesn't account for, requiring human review and repeated/guided runs.
 github.blogarticleAdded 8 Oct 2026, published 28 Sep 2026🧠 AI
 Researchers Detail DifyTap Flaws in Dify That Could Expose AI Chats Across Tenants
Zafran Security disclosed four vulnerabilities (dubbed DifyTap) in the open-source agentic workflow platform Dify, including two critical authorization bypass/path-traversal bugs (CVE-2026-41947, CVE-2026-41948) letting attackers redirect app traces to an attacker-controlled LLM provider or reach Dify's internal Plugin Daemon API, plus two file-preview authz flaws (CVE-2026-41949, CVE-2026-41950) exposing other tenants' uploaded documents and chat files via UUID guessing. Separately, Dify's file-parsing stack bundled a version of PDFium vulnerable to CVE-2024-5846, a use-after-free that can trigger heap corruption via a crafted PDF. All but CVE-2026-41948 were patched in Dify 1.14.2.
 thehackernews.comarticleAdded 26 Sep 2026🛡️ Security
 Mini Shai-Hulud Worm Compromises TanStack, Mistral AI, Guardrails AI & More Packages
The Hacker News details the "Mini Shai-Hulud" campaign by threat actor TeamPCP, which compromised npm and PyPI packages from TanStack, UiPath, Mistral AI, OpenSearch and Guardrails AI via a chained GitHub Actions attack (pull_request_target abuse, cache poisoning, OIDC token extraction), now tracked as CVE-2026-45321 (CVSS 9.6). The worm mints npm publish tokens directly from stolen OIDC credentials to self-propagate — the first documented case of a worm producing validly SLSA Build Level 3-attested malicious packages — and deploys an obfuscated credential stealer with IDE persistence hooks, a GitHub Actions secret-exfiltration workflow, and a dead-man's-switch that runs "rm -rf" if its rogue npm token is revoked. Over 170 packages and 400+ attacker-controlled repos have been identified across npm and PyPI, with findings credited to Aikido Security, Endor Labs, SafeDep, Socket, StepSecurity, Snyk, Wiz and Microsoft.
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security- 973 MCP Packages, 71% Single-Maintainer: A Practitioner
Suzu Labs guide to securing AI developer workflows across three surfaces: AI-generated code (Veracode 45% vulnerable, a formal-verification study at 55.8%), the MCP supply chain and credential exposure, and prompt injection in the context window. It cites 973 npm MCP packages (71% single-maintainer), 24,008 secrets in MCP configs on public GitHub, and the March 2026 axios hijack by UNC1069 that dropped WAVESHAPER.V2 and tampered with MCP configs. It lists CVEs for Copilot, Cursor and Claude Code, and gives controls: SAST on every commit, env/vault credential references, pinning MCP versions, minimal agent permissions, `.cursorignore`/Claude deny rules, and monitoring IDE DNS traffic.
 securityboulevard.comarticleAdded 26 Sep 2026🛡️ Security
 Metasploit Wrap Up: Belgian Waffles, Chocolates, and…Modules-Frites?
Rapid7's weekly Metasploit Framework wrap-up detailing five new modules: an unauthenticated arbitrary file read exploit for GitLab CE/EE (CVE-2026-85706, affecting 18.7–19.1.8/19.2.6/19.3.2), native mitm6-style DHCPv6/IPv6 RA DNS-takeover modules (CVE-2026-20929) used as part of a Kerberos authentication relay attack chain, an authenticated RCE exploit for Langflow's custom components (CVE-2026-18729, versions ≤1.11.1), and a cross-platform persistence module for the Kate text editor. It also covers a ZoomEye search-module fix for the v2 API and nine bug fixes to Metasploit's credential, RDP, and encoder internals.
 rapid7.comarticleAdded 7 Oct 2026, published 25 Sep 2026🛡️ Security
 When chat is the wrong UI
Burke Holland (GitHub) argues that chat is often the wrong interface for working with AI coding agents and introduces "canvas" — a feature in the GitHub Copilot app that spins up a small full-stack application with no browser chrome, which can call third-party APIs or run code locally while exchanging messages bidirectionally with the Copilot agent. He walks through concrete canvases: a playable Connect 4 game against the agent, a Winget package browser/installer, a SQLite query UI with IntelliSense, a Markdown-to-Windows-Live-Writer-style blog editor, and a full development-workflow automation canvas that removes the human from the loop between research, prototyping and review steps. The piece frames this as a general lesson for agent builders: build a reusable tool the agent and user can both interact with, rather than burning tokens asking the agent to perform every repetitive action through chat.
github.blogarticleAdded 8 Oct 2026, published 24 Sep 2026🧠 AI Scan for Good: Using AI to discover and fix high-priority exposures across public services and critical infrastructure
Wiz announces Scan for Good, an initiative that pairs its AI pentester (Red Agent) and Google DeepMind's Gemini 3.8 Flash Cyber with human researchers. It scans authorized public-facing services of critical infrastructure, hospitals, municipalities and nonprofits for exposures and attack paths. It lists anonymized findings, including an exposed admin key over an 8.8M-file archive, NoSQL injection at an AI training-data platform, unsafe upload to hospital server control, and public CI/CD workflows leaking credentials. It also sets out the authorization, human-validation and private-disclosure rules.
wiz.ioarticlePublished and added 24 Sep 2026🛡️ Security Your Vulnerability Backlog Is No Longer Technical Debt, It’s an Attack Surface
A Snyk blog post arguing that vulnerability backlogs traditionally managed as "accepted technical debt" have become genuine attack surface, because AI-accelerated code generation has pushed vulnerability inflow to roughly six new findings per one remediated, unauthored AI-written code removes the "ask the author" triage shortcut, and cheap automated reconnaissance lets attackers walk large backlogs an analyst never would. It illustrates how individually-low-severity findings (an IDOR leaking an internal object ID, a verbose error confirming valid IDs, and an outdated deserialization library) can chain into an authenticated RCE path invisible to severity-based sorting, and argues better prioritization only reorders a backlog rather than shrinking it. It closes with four metrics programs should measure (90-day inflow vs. closure, age of risk-accepted findings, share of human-authored merges, and security-fix merge rate) before promoting Snyk's Evo product.
snyk.ioarticlePublished and added 24 Sep 2026🛡️ Security Engineering a security harness for AI coding agents | Blog | Endor Labs
Endor Labs engineering post arguing that prompts are not security controls and lays out a seven-question framework for building a "security harness" around AI coding/remediation agents: defining the job, minimizing evidence to authoritative facts, tiering authority (Read→Recommend→Prepare→Publish→Enforce), gating consequential actions on proven conditions, evaluating process/result/outcome with contestability, failing closed on interruption or attack, and versioning/owning the agent over time. It illustrates the approach with a controlled dependency-remediation workflow (upgrading Jinja2 with explicit stop-for-approval gates) and cites an internal benchmark where evidence-equipped agents used 91.7% fewer tokens (6.6M vs 79.5M) than agents that had to reconstruct security posture via tool-loop reconnaissance.
endorlabs.comarticlePublished and added 22 Sep 2026🛡️ Security npm Supply-Chain Attack Abuses Trusted Publishing to Ship GHAPPIER Loader
Orca Security details a supply-chain attack on the npm package @dforge-core/dforge-mcp, where a compromised maintainer account modified the GitHub Actions release workflow so any push to main triggered an OIDC-based trusted publish, shipping malicious version 0.2.21 with valid Sigstore provenance. The four-stage GHAPPIER loader activated only when the MCP server launched, deployed a self-deleting remote shell, and per CloudSEK's tracing appeared across 65 repos and 22 accounts; a second payload matched PolinRider, a DPRK-linked campaign using Ethereum transactions for C2. The piece underscores that npm provenance attests build origin, not source integrity, and lists remediation steps since no CVE or advisory yet exists.
orca.securityarticlePublished and added 22 Sep 2026🛡️ Security- Three CVEs and the May 2026 Exploit Chain Nobody's Taking Seriously (nginx Rift)
Analyzes three May 2026 Linux CVEs as one chain: CVE-2026-42945 (NGINX Rift), an unauthenticated heap overflow in ngx_http_rewrite_module (is_args mismatch between length and copy passes), then page-cache LPEs Copy Fail (CVE-2026-31431, authencesn) and Dirty Frag (CVE-2026-43284/CVE-2026-43500, xfrm-ESP/rxrpc) that bypass the algif_aead blacklist. Author releases a bash static scanner for vulnerable rewrite patterns (unnamed captures plus '?' followed by rewrite/if/set) and gives fixes: upgrade nginx to 1.30.1/1.31.0 or use named captures, plus kernel module mitigations.
securityboulevard.comarticleAdded 21 Sep 2026🛡️ Security 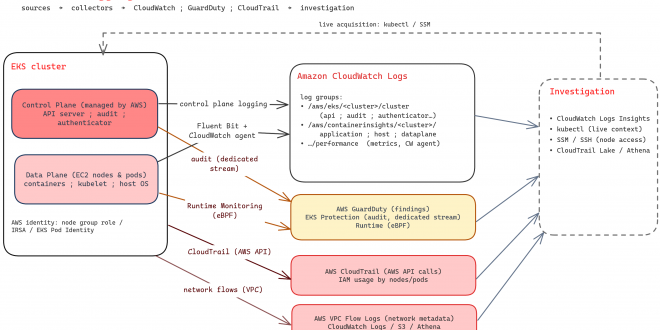 AWS EKS Forensics: Data Sources and Investigation Tooling
Synacktiv's CSIRT breaks down the forensic data sources exposed by Amazon EKS across three layers — Kubernetes control plane (audit logs), data plane (Container Insights/Fluent Bit), and AWS services (GuardDuty EKS Protection, CloudTrail) — and provides concrete CloudWatch Logs Insights queries for RBAC-escalation detection, static pod persistence, node credential theft, and other attack indicators. It also covers node-level acquisition (SSM, kubectl debug), containment pitfalls that destroy evidence, and a full investigation workflow from GuardDuty finding to cross-layer timeline correlation.
 synacktiv.comarticleAdded 21 Sep 2026🛡️ Security
 Securely using pull_request_target - GitHub Enterprise Cloud Docs
GitHub's official guide on securely using the pull_request_target GitHub Actions trigger, explaining how it differs from pull_request by running workflow code and actions/checkout from the base repository's default branch while granting secrets and a privileged GITHUB_TOKEN. It details how "pwn request" vulnerabilities are introduced when workflows check out and execute a fork's pull request head (e.g. via ref: github.event.pull_request.head.sha), describes GitHub's new default policy that blocks pull_request_target in public repos (enforced starting Nov 2 2026), and lists hardening controls including least-privilege GITHUB_TOKEN, read-only cache access, isolated self-hosted runners, and the explicit allow-unsafe-pr-checkout opt-out flag in actions/checkout.
 docs.github.comarticleAdded 21 Sep 2026🛡️ Security
- V7 cuts costs 78% while boosting accuracy with GPT-5.6 Luna
Case study of V7 Go, an agentic workflow platform for finance and insurance. It builds a Context Graph of entities, relationships and cited evidence extracted from SharePoint and Google Drive files, with RAG fallback and an MCP server for querying and ingestion. Workflow steps are tiered across GPT-5.6 Luna (high-volume extraction), Terra and Sol (reasoning and tool use), and GPT-6 Astra (hardest graph queries). Reported results: 78% lower cost per document with Luna versus GPT-5.4 mini, tool-call error rate down from 2.7% (GPT-5.5) to 0.2% (GPT-5.6 Sol), and GPT-6 Astra at 89% versus Sol's 78% on very-hard graph-query questions. V7 also reports ~5% token savings from moving Chat Completions to the Responses API and a 69% gain over the HERB baseline. The figures are vendor and customer reported.
openai.comarticleAdded 29 Sep 2026, published 21 Sep 2026🧠 AI  Hackers breach OpenAI using Claude tools, gaining access to employee accounts and the company
Hacktron AI researchers chained a heap overflow in an outdated libheif library (triggered via a malicious HEIF profile-picture upload on OpenAI's Discourse forum) into remote code execution, then pivoted through an SSO session-isolation flaw to hijack an OpenAI employee's ChatGPT/Codex account and its linked GitHub, Slack, and email access, proving impact with an internal pull request. The exploit code for the heap overflow was generated by Claude Opus 5 (an 'authorized, cybersecurity-configured' variant) after the model was fed raw server data describing the bug, illustrating AI-assisted vulnerability exploitation in a real bug bounty. OpenAI patched within 14 hours and paid a $6,500 bounty; full resolution took 72 hours.
 tomshardware.comarticleAdded 26 Sep 2026, published 18 Sep 2026🛡️ Security
 Workflow execution protections in GitHub Actions generally available - GitHub Changelog
GitHub Actions' workflow execution protections (actor and event allowlist rules) reach general availability, adding workflow-file-level policy targeting, an Insights dashboard for auditing rule impact, and a REST API for managing policy as code across an enterprise. Alongside this, GitHub is rolling out a new secure default that disables the pull_request_target trigger on public repositories lacking an existing policy, directly mitigating 'pwn request' attacks where fork-submitted code runs with base-repo secrets; the rule starts in evaluate (shadow) mode and becomes enforced on November 2, 2026.
github.blogarticleAdded 21 Sep 2026, published 17 Sep 2026🛡️ Security Building an AI Detection Engine That Understands Agent Intent
Wiz describes an AI detection engine that analyzes model input/output telemetry (prompts, system prompts, tool calls, reasoning) rather than just outputs, in order to catch shifts in AI agent intent such as indirect prompt injection. It walks through OpenAI's disclosed Hugging Face/ExploitGym incident and an internal support-agent phishing-relay scenario, then describes a staged pipeline (regex/SLM candidation, light LLM filtering, deep LLM analysis, correlation with cloud/runtime telemetry) validated against a benchmark of 100+ simulated scenarios covering 57 injected attacks and 45 benign workflows across CI/CD, DevOps, data analyst, support, CLI, and cloud auditor agent personas.
wiz.ioarticlePublished and added 17 Sep 2026🛡️ Security GitHub Actions Adds cache-mode to Limit Cache Poisoning Risk
GitHub added cache-mode to Actions, a least-privilege control (read/write/write-only/none) that limits which workflows can restore or save entries in the shared Actions cache, targeting the cache poisoning technique used to compromise Ultralytics (PyPI) and the TanStack npm packages via a pull_request_target pwn request. Job-level settings override workflow-level ones, the mode propagates through reusable workflows, and GitHub warns when write access is granted to low-trust events; write-only was added after feedback from researcher Adnan Khan. The article notes build provenance (SLSA/Sigstore) doesn't catch a poisoned cache since it only attests to build origin, not input integrity, and recommends cache-mode: none for AI agent workflows exposed to prompt injection, referencing the Cline compromise.
 socket.devarticleAdded 21 Sep 2026, published 16 Sep 2026🛡️ Security
 Common C/C++ Vulnerabilities: A Practical Guide to Prevention | Blog | Endor Labs
Endor Labs guide to C/C++ memory-safety and input-handling vulnerabilities — buffer overflow (CWE-787/120/121), use-after-free (CWE-416), null pointer dereference (CWE-476), integer overflow (CWE-190), and format string bugs (CWE-134) — with vulnerable/fixed code snippets for each. It surveys detection tooling (Coverity, CodeQL, Clang Static Analyzer, AFL++/libFuzzer with ASan/UBSan, OSS-Fuzz) and argues that build-system complexity (Bazel, CMake, Conan, vcpkg) and high SAST false-positive rates make reachability analysis necessary, closing with a pitch for Endor Labs' AURI reachability engine.
endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security Combining EPSS and Reachability Analysis to Optimize Vulnerability Management | Blog | Endor Labs
Endor Labs breaks down how the Exploit Prediction Scoring System (EPSS) v3 works — the exploitation telemetry, exploit-DB/GitHub/Metasploit code checks, CISA KEV/Project Zero/ZDI mentions, CVSS vectors, CWE, and social-media signals it ingests to score CVE exploitation likelihood — and shows that an EPSS-threshold (0.088) remediation strategy fixes the same share of exploited CVEs while patching only ~7.3% of known vulnerabilities versus ~82% under a "fix all high/critical" CVSS approach. It then explains a layered workflow: use reachability analysis (call-graph based) to cut findings by ~80% to what's actually exploitable in your environment, then apply EPSS on that reduced set to rank remaining issues by real-world exploitation likelihood, including for third-party/proprietary code where reachability analysis isn't feasible.
endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security Metasploit Wrap Up: This One Goes to Sixteen!
Rapid7's weekly Metasploit Framework update covering sixteen new modules: ten exploits (five on the CISA KEV list) targeting Cisco Secure Firewall Management Center (CVE-2026-20079 auth bypass RCE), SonicWall SMA1000 (CVE-2026-83549 chained RCE), PaperCut NG/MF (CVE-2026-81578 + CVE-2026-82078), JetBrains TeamCity agent-polling XStream deserialization RCE (CVE-2026-63077), Langflow authenticated RCE (CVE-2026-19295), MCPJam Inspector command execution (CVE-2026-23744), SimpleHelp OIDC auth bypass (CVE-2026-48558), Next.js Windows RCE (CVE-2026-75604), and SPIP SQLi/RCE flaws. It also adds a new native Kerberos relay module exploiting ESC8 (AD CS Web Enrollment) via SMB-to-HTTP coercion, a Metasploit handler-detection scanner, a Linux sandbox-evasion module, two Windows persistence techniques, and several bug fixes to the DNS and module metadata subsystems.
rapid7.comarticleAdded 7 Oct 2026, published 11 Sep 2026🛡️ Security- GTIG AI Threat Tracker: From Prompting to Autonomy – The Evolution of Adversarial AI
GTIG AI Threat Tracker for Q2 2026 reports adversaries moving from basic prompting to agentic AI workflows. Cases include a cloud-hosted multi-agent credential harvesting campaign built in under six hours, the "Recon" framework holding over 23,800 stolen secrets, and UNC6780 (TeamPCP) supply chain attacks on PyPI, npm and Docker Hub with prompt injection aimed at LLM scanners. It also covers theft of proprietary AI models, LLMJacking, and Gemini misuse by PRC, Iranian, Russian and DPRK groups.
cloud.google.comarticleAdded 29 Oct 2026, published 8 Sep 2026🛡️ Security






Showing 90 of 151
Show more