 FBI links $6.3 billion Binance crypto heist to North Korean hackers
The FBI attributed the roughly $6.3 billion Binance theft of about 29 October 2026 to North Korea's TraderTraitor (Lazarus Group, Jade Sleet, APT38). Binance traced the breach to a compromised DevOps engineer's laptop that gave access to a service container used to submit unauthorized withdrawals across ten blockchains. The FBI published 628 laundering addresses and linked the group to earlier thefts at Bybit, DMM Bitcoin, Bitget and Drift.
 bleepingcomputer.comarticlePublished and added 1 Nov 2026🛡️ Security
 Alpine Linux rebuilds GitLab after attempted RCE attack
Alpine Linux rebuilt its GitLab server and reset all passwords after attackers tried to exploit CVE-2026-97229, a maximum-severity integer overflow in the Onigmo regex engine bundled with Ruby, on October 20-21. Eight worker crashes occurred and four were partially successful. Missing logs and outbound connection records meant compromise could not be ruled out. Alpine had run GitLab 19.3.4, then 19.3.6, which lacked the Ruby patch; the fixed image is alpinelinux/gitlab:19.3.6 with Ruby 3.3.13.
bleepingcomputer.comarticlePublished and added 1 Nov 2026🛡️ Security- Binance Replaced 90% of Assets Stolen in the $6.3B Binance Crypto Hack
Report on the $6.3 billion Binance hack of October 2026, which the FBI attributed to North Korea's TraderTraitor unit. Co-CEO Richard Teng said attackers used EIP-7702 to gain execution approval over a hot wallet, after a compromised laptop and further breach points, and used self-destructing malware. Binance replaced 90% of the assets, and the FBI expects further laundering through Ethereum. No IOCs or mitigations are given.
 en.cryptonomist.charticleAdded 1 Nov 2026, published 31 Oct 2026🛡️ Security
 Binance Hack: Everything You Need to Know About the Biggest Crypto Heist in History
Decrypt's explainer on the roughly $6.4 billion theft from Binance hot wallets across about 10 blockchains. Binance traced it to a compromised DevOps engineer laptop plus further breach points, and on Ethereum the attacker used 50 pre-signed EIP-7702 authorizations to turn a hot wallet into a sweeper. Chainalysis and TRM Labs attribute it to TraderTraitor; Tether and Circle froze about $2.3 billion.
 decrypt.coarticlePublished and added 31 Oct 2026🛡️ Security
 Syrian Hacker Gets Prison Time in US After Over a Decade on the Run
Ahmad Umar Agha (Th3Pr0), a Syrian Electronic Army member, received a 42-month US sentence in the Eastern District of Virginia, over 12 years after he was first charged in June 2014. He compromised about 47 Western media, company, NGO and government targets, including the 2013 Associated Press Twitter takeover that caused a flash crash. Accomplice Firas Dardar remains at large.
 securityweek.comarticlePublished and added 31 Oct 2026🛡️ Security
 Binance’s $6.3 Billion Hack Puts Developer Machine Security in Focus
StepSecurity's analysis of Binance's 29 October 2026 incident, which Binance puts at about $6.3 billion in affected assets. It covers Binance's disclosure of a possible DevOps laptop compromise, and TRM Labs and Elliptic findings on 50 EIP-7702 authorizations and a persistent delegation. It links this to the Nx, OVHcloud CLI and Claude Code extension compromises, gives an investigation checklist, then describes StepSecurity products.
 stepsecurity.ioarticlePublished and added 30 Oct 2026🛡️ Security
 ERC draft: Independent Simulation Result for (STVA)
ERC draft "Independent Simulation Result" (STVA) defines a canonical, content-addressed SimulationResult (success, gasUsed, returnData, stateDiffHash, logsHash, snapshotId, resultHash) that any wallet, hardware device or verifier can recompute from the same VerificationPayload and state snapshot. It targets compromised-frontend and UI/calldata-mismatch attacks, and defines Basic, Standard and Strict compliance levels. Open questions are stateDiff encoding, prestate proofs and binding to capability tokens.
 ethresear.chthreadPublished and added 30 Oct 2026🛡️ Security
- President Trump says they’re looking into Binance hack as calls grow for crypto rules
The Block reports that Binance lost about $6.3 billion in a hack on 29 October 2026. Co-CEO Richard Teng said a compromised DevOps engineer's laptop gave access to a service container used to submit unauthorized withdrawals, and TRM Labs attributed the theft to North Korea's TraderTraitor. The rest covers reactions: President Trump said on 30 October he was looking into it, CFTC Chair Michael Selig and The Digital Chamber urged federal exchange rules, and senators disputed whether the Clarity Act would have allowed freezes.
 theblock.coarticlePublished and added 30 Oct 2026🛡️ Security
 Weekly Research Brief: Binance Hacked; Hyperliquid on Wall Street; Prediction Markets’ Brazil ‘Miss’
Galaxy Research's weekly brief of 30 October 2026 opens with the Binance hack: about $6.3b drained across 10 blockchains, attributed by TRM Labs and Chainalysis to TraderTraitor (Lazarus-linked). The attacker used EIP-7702 with 50 pre-signed authorizations on Ethereum, and Binance's preliminary finding is a compromised DevOps laptop reaching a service container. Tether and Circle froze about $2.6b. The other sections cover Hyperliquid and prediction markets.
 galaxy.comarticleAdded 30 Oct 2026🛡️ Security
 Here We Go Again: Binance Loses $6.3b in Largest Robbery in History
Galaxy Research newsletter on the roughly $6.3b drained from Binance across 10 blockchains, which TRM Labs and Chainalysis attribute to TraderTraitor. On Ethereum the attacker used EIP-7702 to turn a hot wallet into a sweeper contract backed by 50 pre-signed authorizations. Binance's preliminary finding is a compromised DevOps laptop, with no wallet key leak. Tether, Circle, Ripple and World Liberty froze about $2.7b; Galaxy also assesses Binance's ability to cover losses.
galaxy.comarticleAdded 30 Oct 2026🛡️ Security Binance Just Suffered the Biggest Hack in Crypto History. What Now?
Bankless report on the Binance hack of $6.3 billion, which Binance's preliminary investigation traced to a compromised DevOps engineer's laptop with access to withdrawal-authorizing systems. TRM Labs found valid EIP-7702 authorizations on Ethereum, and nine other chains were drained through normally signed transactions. TRM and Chainalysis link it to North Korea's TraderTraitor. Tether and Circle froze about $3 billion, and Binance says SAFU and corporate cash will cover the losses.
 bankless.comarticlePublished and added 30 Oct 2026🛡️ Security
 Polymarket Sends $3.9M Back to Traders After Vendor Script Drain
Polymarket's international site was hit on 29 October 2026 when a page-speed monitoring script served from DebugBear's CDN was replaced with a drainer. It hijacked logged-in sessions for about an hour and took $2.7M from 726 wallets via Polymarket's relayer. Scott Helme of Report URI says the CSP allowlisted every domain used and that hash pinning would have blocked the swapped file. Polymarket is repaying $3.9M, and this is its second vendor-script compromise since June.
bankless.comarticlePublished and added 30 Oct 2026🛡️ Security Secret Service, FBI Join Binance Hack Probe as Circle Freezes $823 Million
Decrypt reports that Binance is working with the FBI and U.S. Secret Service after a theft of about $6.4 billion, which TRM Labs and Chainalysis attribute to North Korea's TraderTraitor group, also linked to the February 2025 Bybit hack. Circle froze about $823 million in USDC and Tether froze USDT, though the page gives differing Tether totals. Binance first suspected a compromised DevOps engineer laptop, found more breach points, and saw no evidence of leaked wallet private keys.
decrypt.coarticlePublished and added 30 Oct 2026🛡️ Security- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA added two Ivanti Connect Secure vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog on 30 October 2026, citing evidence of active exploitation: CVE-2026-111357 (missing authentication for a critical function) and CVE-2026-118527 (generation of predictable numbers or identifiers). The alert restates BOD 26-04, which requires federal civilian agencies to remediate KEV-listed flaws on exposed assets and check for prior compromise. It also links the KEV nomination form.
 cisa.govadvisoryPublished and added 30 Oct 2026🛡️ Security
 EIP Draft: Permanent EOA Delegation Opt-Out (disable EIP-7702)
Discussion thread for a draft Core EIP that lets an Ethereum EOA permanently disable EIP-7702 delegation. A type-4 set-code transaction with an empty authorization list, destination equal to sender and zero value installs the 0xef0200 marker for 33500 gas. Later authorizations, including clearing to the zero address, are skipped. It does not protect against private-key compromise. Open questions cover the prefix, a dedicated transaction type, gas pricing, and EIP-8151 interaction.
 ethereum-magicians.orgthreadPublished and added 30 Oct 2026🛡️ Security
 Binance Sets Aside $6.34B to Cover Hack Losses, CEO Says 'Your Assets Are Safe'
Decrypt reports on the October 2026 Binance hot-wallet hack, about $6.3 billion, which Binance CEO Richard Teng says the company will cover with over $6.34 billion of its own funds. Teng says the attacker used an EIP-7702 delegation that skipped Binance's approval controls, a self-destruct mechanism to wipe tooling, and more than one breach point beyond a compromised laptop. TRM Labs and Chainalysis attribute the theft to TraderTraitor, and the attacker is still moving funds on Tron.
decrypt.coarticlePublished and added 30 Oct 2026🛡️ Security- PHP2Shell Attacks Root Palo Alto Firewalls but Fail Against WordPress
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) has been exploited for over a week. A China-linked group chained it with the Fragnesia Linux kernel privilege escalation to root at least 25 Palo Alto Networks PAN-OS firewalls with exposed management interfaces. Defiant had seen no confirmed WordPress compromise by 28 October 2026 despite 77,000 requests, and Cato and watchTowr report few successful attackers.
securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security  Binance hack: the largest robbery in financial history
Binance hack analysis from 21shares on the 29 October 2026 theft of about $6.3 billion from Binance. Binance's initial finding points to a compromised DevOps engineer's laptop with no sign of a leaked wallet key. Chainalysis attributes it to North Korea with high confidence, and about $3 billion was frozen by Tether, Circle and the Arbitrum Security Council. The attacker also borrowed about $44.6 million of WETH on Aave. Binance says SAFU and company funds will cover all losses.
 21shares.comarticlePublished and added 30 Oct 2026🛡️ Security
- Binance says it has $6.34 billion ready to cover hack losses
The Block reports that Binance says it has set aside $6.34 billion of its own funds to cover a hack it puts at about $6.3 billion. Co-CEO Richard Teng says the entry point was a compromised DevOps laptop and no private key leak was found. About $3 billion was frozen by Tether, Circle, Ripple and others, withdrawals are suspended, and TRM Labs sees parallels with North Korean attacks. Technical detail is thin.
theblock.coarticlePublished and added 30 Oct 2026🛡️ Security  Binance hack: how a compromised developer laptop can lead to a $6.3 billion breach
Aikido Security's analysis of the roughly $6.3 billion Binance incident, which Binance says may have started with a compromised DevOps engineer's laptop. It sets out what is known (no private key leak, TraderTraitor attribution by TRM Labs and Chainalysis, additional breach points) and a plausible chain from laptop credentials to a withdrawal service. It compares the 2025 Bybit theft and lists mitigations.
 aikido.devarticlePublished and added 30 Oct 2026🛡️ Security
 TRM and Chainalysis Tie $6.4B Binance Hack to North Korea's TraderTraitor
TRM Labs and Chainalysis attribute the October 2026 Binance theft, about $6.4 billion across 10 blockchains, to North Korea's TraderTraitor. On Ethereum the attacker used EIP-7702 delegation with 50 pre-signed authorizations to turn a hot wallet into a sweeper, pointing to compromised signing infrastructure. The attacker funded wallets via Tornado Cash, laundered through automation and Aave borrowing, and about $3 billion was frozen.
decrypt.coarticlePublished and added 30 Oct 2026🛡️ Security Fresh WordPress Vulnerability in Attackers’ Crosshairs
A WordPress core race condition in the update process, patched in WordPress 7.1.4 on 28 October 2026, allows unauthenticated remote code execution with high attack complexity. New files unpack into a predictable, web-accessible staging directory. Defiant's Wordfence logged over 18,500 requests for staged setup-config.php paths in 21 hours, with no confirmed compromises. No CVE is assigned yet. The release fixes 22 flaws in total.
securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security- Backdoors in official Claude Code extensions
GossiTheDog's Mastodon post reports that the Anthropic Claude Code Visual Studio extension, as installed in Cursor, contains malware that creates a remote access Trojan on desktops. It links to a phorion.io blog post on the reported compromise of the official Claude Code VSX extension. The post gives no technical detail, indicators or dates itself.
 cyberplace.socialthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
 Binance Finds 'Additional Points of Breach' in $6.3B Hack
Binance estimated the October 2026 security incident at about $6.3 billion and said it found "additional points of breach" beyond the compromised DevOps engineer laptop it first named. The attacker reached a service container and submitted unauthorized withdrawals, with no wallet private key leak found. Arkham counted $6.01 billion taken from hot wallets on nine chains; Tether and Circle froze about $1.8 billion in stablecoins. About $3 billion is frozen onchain; withdrawals stay suspended.
decrypt.coarticlePublished and added 30 Oct 2026🛡️ Security Binance links $6.3 billion crypto theft to compromised DevOps laptop
Binance linked the theft of about $6.3 billion in crypto to a compromised DevOps engineer's laptop, which let attackers reach a service container and submit unauthorized withdrawals. TRM Labs and Chainalysis attribute the 29 October 2026 attack to North Korea's TraderTraitor. About $2.7 billion was frozen, and the attackers hold about $2.4 billion. Binance has found no evidence of a leaked wallet private key.
bleepingcomputer.comarticlePublished and added 30 Oct 2026🛡️ Security TeamViewer Flaw Could Let Malicious Hosts Take Over Support Technicians’ Machines
CVE-2026-111585 (CVSS 8.8) is an integer overflow in the remote-control screen processing of TeamViewer clients on Windows, macOS, Linux and Android. A malicious or compromised host can announce an oversized screen surface (for example 32768 by 32768 at 32 bpp), forcing a software decode path and an out-of-bounds write that crashes the viewer or runs code. Remedio's research shows a pointer overwrite routed to WinExec. Version 15.83 fixes it, along with CVE-2026-92372, CVE-2026-92374 and six local privilege escalation bugs.
securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security $6 Billion Binance Hack Bears Hallmarks of North Korea’s TraderTraitor
The Binance hack of 29 October 2026 drained about $6.36 billion across ten blockchains in roughly 20 minutes, according to TRM Labs. TRM attributes it with high confidence to North Korea's TraderTraitor, citing a mixer-funded operator wallet, pre-signed transactions and overlap with the Bybit and KelpDAO hacks. Binance's early findings point to a compromised DevOps engineer laptop. Stablecoin issuers froze about $2.7 billion.
securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security Binance probes a suspected cryptocurrency breach: $6.3B affected, about $3B frozen
Binance disclosed a suspected security incident on 29 October 2026, estimating $6.3 billion affected and about $3 billion frozen. Binance's early finding is that a compromised DevOps engineer's laptop let an attacker reach a service container and submit unauthorized withdrawals, with no evidence of wallet private-key leakage. TRM Labs suspects TraderTraitor, the group tied to the February 2025 Bybit theft. Tether, Circle and Ripple froze funds.
en.cryptonomist.charticlePublished and added 30 Oct 2026🛡️ Security- ERC draft: Independent Simulation Result for (STVA)
ERC draft "Independent Simulation Result" (STVA) defines a canonical, content-addressed SimulationResult structure that wallets, hardware devices or third-party verifiers can recompute from the same VerificationPayload and state snapshot. It specifies fields, a keccak256 or EIP-712 result hash, and Basic, Standard and Strict compliance tiers. The goal is to close UI/calldata mismatch attacks where a compromised frontend serves a false simulation. Open questions cover stateDiff encoding and prestate proofs.
ethereum-magicians.orgotherPublished and added 30 Oct 2026🛡️ Security - llm-trails: What LLMs reach for inside a breached AWS account
llm-trails is an open study of what LLMs choose to do next inside a breached AWS account. It puts 14 models in 13 post-compromise situations, records only a single-turn plan with nothing executed, and codes each answer to CloudTrail events. The repo has the llmtrials harness, prompts, codebook, processed dataset (viz_data.json) and an interactive dashboard, so the study can be rerun or extended.
 github.comrepoAdded 30 Oct 2026🧠 AI
- llm-trails: What LLMs reach for inside a breached AWS account
llm-trails is a research repo that placed 14 LLMs in 13 post-compromise AWS situations, asked only for their next move (single-turn, nothing executed), and coded each answer to CloudTrail events. It includes the llmtrials harness, prompts, codebook, processed dataset (viz_data.json) and an interactive dashboard. Rates are conditioned on the situation shown, and the aim is turning model behavior into detection priorities.
github.comrepoAdded 30 Oct 2026🛡️ Security  Trail of Bits (@trailofbits) on X
Trail of Bits post on X summarising Binance's initial investigation into a security incident. Binance suggests a compromised DevOps engineer's laptop let an attacker reach a service container and submit unauthorized withdrawal transactions. The text says no evidence has been found of wallet private key compromise. The fetched text is truncated and gives no further detail.
 x.comthreadPublished and added 30 Oct 2026🛡️ Security
 Polymarket stolen funds: One account withdrew at least $2.7M across 710 wallets
Polymarket's international exchange suffered unauthorized withdrawals on 29 October 2026 after a compromised third-party provider, reportedly the website monitoring service DebugBear. Betting Intelligence and Polysights found one account withdrew at least $2.7 million across 710 wallets. Polymarket paused trading, referred the case to law enforcement, promised reimbursement, and had a June 2026 vendor breach that cost about $3 million. The attack mechanism is not described.
en.cryptonomist.charticlePublished and added 29 Oct 2026🛡️ Security Polymarket Pauses Trading as Prediction Market Investigates Security Incident
Polymarket put its exchange in cancel-only mode and paused relayer actions on 29 October 2026 after users reported funds withdrawn without permission. Hudson Rock says a DebugBear-hosted script holds wallet-draining code that sells a logged-in user's positions and hard-codes the suspected attacker's wallet (about $2.65 million in POL, per Arkham) as fallback recipient. Polymarket blames a compromised third-party provider and promises to make users whole. Root cause and victim count are unconfirmed.
decrypt.coarticlePublished and added 29 Oct 2026🛡️ Security Hackers Publish Work Details of 41,000 Homeland Security Employees
Icepick is a dataset published on 28 October 2026 by Distributed Denial of Secrets. It lists 41,191 DHS employees and contractors with names, titles, offices, phones, managers and 55,000+ permission groups. The hacktivist group Department of Peace says it took the data from DHS's Okta SSO; Okta denies compromise. DHS has filed a takedown notice via ZeroFox, and the full archive is unverified.
decrypt.coarticlePublished and added 29 Oct 2026🛡️ Security Threat Brief: Critical Vulnerabilities in PHP: CVE-2026-109618, CVE-2026-109619 (Updated October 29)
Unit 42 threat brief on PHP2Shell, two PHP remote code execution flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS 4.0 9.2), both caused by longjmp() error handling that leaves memory uninitialized or freed. Cortex Xpanse counted over 22.6 million exposed instances. The 29 October 2026 update says attackers chained PHP2Shell with a Linux kernel privilege escalation against internet-exposed PAN-OS management interfaces. An earlier 23 October claim of post-compromise activity was retracted on 25 October.
 unit42.paloaltonetworks.comadvisoryAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 [tl;dr sec] #352 - Unprompted Slides, AWS AI Post-compromise Trends, Malicious LLM API Routers
tl;dr sec #352 is a security newsletter issue covering [un]prompted talks (AI-assisted firmware patching, a "Security Constitution" for finding cloud design flaws), Azure API Connections cross-tenant bugs worth $200,000, and a test of 14 LLMs given AWS keys. It also covers a paper on malicious LLM API routers (9 of 428 injecting code) and Datadog's "counterfeit policy" bypass of the Jev classifier.
 tldrsec.comarticleAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 The Rise of Agentic Attacks: What They Look Like, and Where They're Headed
Wiz research on intrusions where AI agents do the hands-on attacker work. It reviews public cases (ARTEX against South Korean banks and the ConnectWise compromise, Hermes at Thailand's Ministry of Finance, JPCERT/CC, CrowdStrike, DIVD) and three Wiz-investigated attacks. It distills fingerprints: machine-paced iteration, embedded natural-language reasoning, self-correcting scripts, checklist enumeration, noisy lateral movement, probe-before-payload habits and self-named scratch files. It also covers attribution, scale and defense implications.
 wiz.iowriteupPublished and added 29 Oct 2026🛡️ Security
 Over 41,000 DHS Employee Records Leaked Online
A hacker using the handle Department of Peace leaked more than 41,000 US Department of Homeland Security employee records, which the hacker says came from an Okta single sign-on system. The data covers names, work emails, phone numbers, job titles, office locations and per-account system access, mostly for CBP, ICE and HSI staff plus about 1,000 CISA employees. Okta says it has no evidence of compromise. Distributed Denial of Secrets calls the dataset 'Icepick'.
securityweek.comarticlePublished and added 29 Oct 2026🛡️ Security- Cryptanalysis and Enhancement of VTBSAE: Provably Secure Verifier-Based PAKE Protocols for the Industrial Internet of Things
Cryptanalysis of VTBSAE, a verifier-based PAKE protocol for the Industrial Internet of Things, showing it fails to resist client impersonation after server compromise. The authors propose E-VTBSAEv1, which binds the client point E1 to fresh server randomness, and prove AKE security and forward secrecy in the random-oracle model under CDH. Raspberry Pi 4B tests show runtime comparable to VTBSAE with the same communication and storage overhead.
 eprint.iacr.orgpaperAdded 31 Oct 2026, published 29 Oct 2026🛡️ Security
 The OpenSourceMalware Show #27
 (28 October 2026) is a podcast episode with transcript. It covers the Brotli decoder bug (CVE-2026-111497) vendored in C code across Python, Rust and PHP, and how to find copies via decode.c. It also covers the LiteLLM v1.107.0 compromise from an unrevoked admin key and a relaxed release control, and the MALFEX npm campaign hiding payloads in PNG-header files, plus an AGENTS.md lure and DPRK fake fonts in TTF/OTF.
 opensourcemalware.comtalkPublished and added 29 Oct 2026🛡️ Security
 Leak Exposes 41,000 Homeland Security Workers–Including Undercover ICE Agents
Icepick is a leaked archive of records on more than 41,000 Department of Homeland Security employees and contractors, published by Distributed Denial of Secrets in 2026 and said to come from DHS's Okta login system. WIRED's analysis covers CBP, ICE, HSI, USCIS and CISA staff, plus over 55,000 permission groups that reference undercover programs, Palantir Falcon, PenLink, Signal and Mobile Fortify. Okta says it has no evidence of compromise.
 wired.comarticleAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security
- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 28 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities Catalog on evidence of active exploitation: CVE-2026-41709 (Broadcom VMware ESX insufficient logging) and CVE-2026-46300 (Linux kernel missing variable initialization). It restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise. It also links the KEV nomination form.
cisa.govadvisoryAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security  Social Engineering: Modem-Based Persistence in a Compromised Environment
The article describes reflashing a Huawei E3372h-153 HiLink 4G USB modem so its embedded Linux OS runs an OpenVPN client over the mobile network, creating a covert, network-independent persistence channel after physical USB access. It walks through enabling debug mode, flashing firmware, disabling CD-ROM emulation, configuring DHCP and autorun scripts, and chaining a second L2VPN tunnel to bridge the attacker directly onto the victim's Ethernet segment for tools like Responder. Defense guidance focuses on restricting USB ports and disabling USB network adapters via policy.
 hackers-arise.comwriteupPublished and added 28 Oct 2026🛡️ Security
 From Leniency to Suspicion: How an Open Post-Training Recipe Changes Whom LLM Fact-Checkers Believe
This paper measures job-based doubt in LLM fact-checkers: judging a claim false more often when the poster has a lower-status job. It compares base and post-trained checkpoints of six model families on fact-checked claims with randomised poster profiles. Only the open Tülu-3 recipe (OLMo-2 32B, Tülu-3 70B) creates the effect, under one percentage point but reliable. In OLMo-2 32B the flip comes from one residual-stream direction and appears at supervised fine-tuning, confirmed on 400 new claims. None of seven commercial models doubts lower-status posters more.
 arxiv.orgpaperAdded 30 Oct 2026, published 28 Oct 2026🧠 AI
- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 27 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities (KEV) Catalog on evidence of active exploitation: CVE-2026-48356, an unrestricted upload of a dangerous file type in Adobe Commerce and Magento, and CVE-2026-111497, an unchecked return value in Google Brotli. It restates BOD 26-04, which makes federal civilian agencies prioritise KEV flaws on exposed assets and check for prior compromise. No technical detail or IOCs are given.
cisa.govadvisoryAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security - Camera Management Software Compromise Leads to Malware Deployment
Huntress investigation of incidents in September and October 2025 where a compromised camera management application (CMS.exe) was the initial access vector. Attackers dropped rs.win32.exe, a reverse shell, and sideloaded modified zlib DLLs (IPHLPAPI.DLL, samcli.dll) via the legitimate Microsoft WpcMon.exe in AppData, with Run key persistence and beaconing to 144.172.116[.]37. Includes detection pivots and hardening advice.
 huntress.comwriteupAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security
 Unexplained DreamHost Incident Prompts Email, FTP Password Resets
DreamHost suspended its File Manager (files.dreamhost.com) and reset passwords for some email and FTP/SFTP users after an unexplained issue affecting File Manager and webmail. Account owners were told to set new passwords and change reused ones; users questioned whether passwords were compromised or properly hashed. DreamHost deployed a fix on Monday. Root cause and number of affected users were not disclosed.
securityweek.comarticlePublished and added 27 Oct 2026🛡️ Security- Prasenjit Sarkar (@stretchcloud) on X
Campfire is a self-hosted tool that runs Claude Code, Codex, Goose, Aider and OpenHands in one tab. Risky actions need permission voting (majority approves, any single deny blocks, 30 second timeout), and session replay traces which file or tool call triggered an action. The post cites Forever Security's finding that Codex followed a planted AGENTS.md instruction over 90% of the time and Claude Code about half the time. It also cites the February Cline release compromise via a poisoned GitHub Actions cache.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security  How to patch PHP2Shell with free Aikido Images
Aikido Images are free patched PHP container images on public ECR (public.ecr.aws/aikido-dev/php) that backport the PHP2Shell fixes for CVE-2026-109618 and CVE-2026-109619 into release lines 5.5 to 8.5, except 8.0. Upstream fixed 8.2 to 8.5 in October 2026 and left 8.1 and older unpatched. The post shows docker pull and Dockerfile FROM changes, then rebuild, restart, session.upload_progress.enabled=0 and compromise checks.
aikido.devarticlePublished and added 26 Oct 2026🛡️ Security- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA added two PHP vulnerabilities to its Known Exploited Vulnerabilities Catalog on 26 October 2026: CVE-2026-109618 (memory corruption) and CVE-2026-109619 (stale internal request state). It also updated its PHP alert on critical vulnerabilities requiring immediate patching. The alert restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise.
cisa.govadvisoryAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security  Keystone to destroy almost 19,000 wallets after device key leak
Keystone confirmed a breach of Shopify customer records (about 26,000 plus 13,000 incomplete orders), in which the attacker also took the WebAuth key used to verify device authenticity. It will destroy almost 19,000 unshipped wallets and issue a new key. Foundation Passport phishing emails (over 20,000) came from compromised Cloudflare API keys, and old WooCommerce database copies kept personal data past the stated 60-day deletion.
 protos.comarticlePublished and added 26 Oct 2026🛡️ Security
 David Gutierrez | Eng (@david_x_ai) on X
Thread on two October 2026 npm compromises: @subql/common 5.8.3 (5 October), published through GitHub Actions OIDC Trusted Publishing after the attacker tampered with the publish workflow, and tensorlake 0.5.144 (8 October), published by the project's own release workflow with valid provenance for about 1 hour 40 minutes. Both ran on install and stole cloud, GitHub, Kubernetes, Vault, SSH and .env credentials; tensorlake also took AI tool and MCP config. Its payload installed a gh-token-monitor service that deletes the home directory if the stolen GitHub token is revoked, so remove it before rotating.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security Clean-label poisoning attack can fool vehicle-network AI without changing labels
Clean-label poisoning attack on federated learning for Basic Safety Message anomaly detection in vehicular networks, from Sagduyu, Erpek, Stephenson and Xue (paper submitted 23 October 2026). The attack perturbs benign samples toward malicious feature extremes without changing labels, which lowers class separability, and it grows stronger with more compromised nodes. A feature-consistency relabeling defense keeps attack success low without hurting clean accuracy, and a game-theoretic model shifts equilibria against attacking.
en.cryptonomist.charticlePublished and added 26 Oct 2026🛡️ Security- Keystone customers say breach exposed data the hardware wallet maker promised to delete
Keystone, a hardware wallet maker, disclosed on 25 October 2026 that an attacker accessed its Shopify-based store, detected 20 October and confirmed 23 October. Customer names, contact details, shipping addresses and order details were taken. Keystone says no payment data, recovery phrases or keys were exposed. Customers on X say their data was held despite a 180-day deletion pledge. The piece lists 2026 leaks at Trezor, SafePal and Ledger.
theblock.coarticlePublished and added 25 Oct 2026🛡️ Security  Podcast: Kimi K3.1 Pro, the new cyber reality, and Muse musings
Interconnects podcast with Nathan Lambert and Florian Brand on Kimi K3.1 Pro and the AI cyber landscape. Kimi says it down-weighted cyber data in mid-training so its open weights do not extend offensive capability. They discuss the PHP2Shell remote code execution bug, the repeat LiteLLM compromise from an API key left in GitHub for five months, abliterated model APIs, and trusted-access programs from OpenAI and Anthropic. The transcript was truncated at the very end.
 interconnects.aitalkPublished and added 25 Oct 2026🛡️ Security
 OVHcloud CLI Compromised via GitHub Release Swap: Detonating the Real GlassWorm Loader and What We Found
Analysis of the 19 October 2026 swap of binaries on five ovh/ovhcloud-cli GitHub releases (v0.11.0 to v0.15.0), live 94 minutes. StepSecurity rebuilt the attacker's binary, detonated the recovered GlassWorm preinstall.js loader against a controlled Solana dead drop, and found install.sh never exposed arm64 Linux, Homebrew was safe, and `ovhcloud version` showing "undefined" identifies the swapped build. Includes IOCs and recovery steps.
stepsecurity.iowriteupPublished and added 24 Oct 2026🛡️ Security [AINews] Kimi 3.1 Pro 104BA-2.8T: Fable-5.1-Class Open Weights narrows Closed-AI lead to 1 month... and Pro Highspeed API with 2-3× speed
AINews digest for 22 to 23 October 2026, led by Moonshot's Kimi K3.1 Pro (2.8T parameters, 104B active, weights promised for 4 November 2026). It reports Artificial Analysis scoring the model 64% on its Cyber Index despite Moonshot removing cyber data from training. Other items: OpenAI's frontier-training containment incident, a Brotli remote-code-execution disclosure, and Anthropic's Mythos 5 unauthorized-action analysis.
 latent.spacearticleAdded 30 Oct 2026, published 24 Oct 2026🛡️ Security
 [AINews] Kimi 3.1 Pro 104BA-2.8T: Fable-5.1-Class Open Weights narrows Closed-AI lead to 1 month... and Pro Highspeed API with 2-3× speed
AINews issue for 22 to 23 October 2026 centred on Moonshot's Kimi K3.1 Pro, a multimodal mixture-of-experts model with 2.8T total and 104B active parameters and 1M context. Weights are promised for 4 November 2026. Artificial Analysis scored it 55 on its Intelligence Index (fourth place), and Arena ranked it #8 in WebDev. Standard pricing is $2/$10 per million tokens. The issue also covers a cyber-data removal approach, serving-cost objections, and paid-promotion allegations. Shorter items follow on agents, evals and inference.
latent.spacearticlePublished and added 24 Oct 2026🧠 AI Prasenjit Sarkar (@stretchcloud) on X
Post on the LiteLLM supply-chain compromise. Attackers spent eleven days in the GitHub org, ran a workflow on a throwaway branch to take twenty secrets including a GitHub App private key, then used stolen GitHub CLI OAuth tokens to publish malicious release 1.107.0 from a lookalike Berri-AI repo. A Python startup file harvested sixteen credential categories and LiteLLM proxy Postgres provider keys. Socket flagged the wheels in seven minutes.
x.comthreadAdded 26 Oct 2026, published 24 Oct 2026🛡️ Security- AI Quanting (@AIQuanting) on X
AI Quanting's X thread covers Moonshot's Kimi K3.1 Pro release (1M-token context, open weights promised by November 4). Moonshot removed cyber data from mid-training and RL stages; on its in-house xdev-bench-hard exploit benchmark (Linux kernel, Node.js, JavaScriptCore, Exim, VirGL bugs) pass@3 fell from 90.5% to 81.0%. The author argues this is only about a tenth of the capability, so four in five expert exploit tasks remain solvable.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🛡️ Security  Hajrë Hyseni | AI for Business (@hajra) on X
Kimi K3.1 Pro is a new model from Moonshot AI. According to a post by hajra, Artificial Analysis ranks it 4th in the world, 3 points behind Claude Opus 5.5. The API price is down by a third, and full open weights are promised by 4 November. The post gives no benchmark breakdown, licence or architecture details.
x.comthreadPublished and added 24 Oct 2026🧠 AI Introducing Kimi K3.1 Pro
Kimi K3.1 Pro is Moonshot AI's new model, available on the Kimi API from 23 October 2026, with full weights promised by 4 November 2026. Pricing is $2.00 per million input tokens and $10 per million output, and a Highspeed variant is 2-3x faster at twice the price. Artificial Analysis scores it 55, behind only Claude Opus 5.5 (58). Simon Willison tested it with the llm CLI and pelican SVG prompts.
 simonwillison.netarticlePublished and added 23 Oct 2026🧠 AI
 Inside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks
Microsoft's analysis of the LiteLLM 1.107.0 compromise, published to PyPI and container images on 21 October 2026. The wheel shipped cook.pth, cook.py and sitecustomize.py, so a credential collector (PRIVCOLLECT) ran whenever Python started, even without importing LiteLLM. It covers AES/RSA-encrypted exfiltration to litellm.dev, a re-armable Unix loader, Defender KQL hunting queries, ATT&CK mapping and rotation guidance.
 microsoft.comwriteupPublished and added 23 Oct 2026🛡️ Security
 Mirai Botnet Operators Join PHP2Shell Attacks as ASLR Bypass Exploits Emerge
PHP2Shell (CVE-2026-109618 and CVE-2026-109619, CVSS v4.0 9.2) are unauthenticated RCE bugs in PHP, patched on 21 October 2026. Sophos, Arctic Wolf and Hunt.io tie exploitation attempts to the Potassium Mirai variant, and VulnCheck built an ASLR-bypassing exploit. SOCRadar and Hunt.io found an exposed attacker server, and Qualys data shows about 110 million instances on end-of-life PHP. No confirmed compromise exists.
securityweek.comarticlePublished and added 23 Oct 2026🛡️ Security LiteLLM Compromised in Fresh Supply Chain Attack
LiteLLM version 1.107.0 was published with malware to PyPI and Docker Hub on October 21, for about three hours and roughly 49,000 downloads. Attackers used GitHub CLI OAuth tokens, likely leaked through Claude Code into LiteLLM logs, to disable branch protections, redirect the releaser to a lookalike repository and sign poisoned artifacts. The payload is an infostealer and RAT; Wiz saw Amazon Bedrock abuse. The last clean version is 1.106.2.
securityweek.comarticlePublished and added 23 Oct 2026🛡️ Security eMudhra / emSign CA Compromise: What Python, pip, and CI/CD Users Need to Update
Guidance on the October 2026 eMudhra / emSign CA incident, where eight intermediate CA certificates had private keys generated with insufficient randomness. It explains why updating certifi alone does not fix pip's vendored bundle, and lists fixed versions (certifi 2026.10.19, pip 26.2.2, Python 3.15.1, 3.14.9, 3.13.17). StepSecurity's OpenSSL 4.0.3 tests showed the older bundle accepted seven emSign paths, while both corrected bundles rejected all fourteen.
stepsecurity.ioarticlePublished and added 22 Oct 2026🛡️ Security- Dark Web Intelligence (@DailyDarkWeb) on X
LiteLLM suspects its October 21 release compromise began with Claude Code responses containing GitHub CLI OAuth tokens that were written to logs of an internet-facing internal LiteLLM gateway. Attackers allegedly stole those tokens, used an organization-owner token to disable branch protections, and pushed poisoned artifacts from a lookalike repository. How they entered the gateway is unconfirmed, and this is not a proven Claude Code vulnerability.
x.comthreadAdded 25 Oct 2026, published 22 Oct 2026🛡️ Security  EMudhra Intermediate CA Certificates Compromised
Unit 42 advisory on the compromise of eight intermediate CA private keys belonging to Indian CA eMudhra Limited. The keys were generated with insufficient randomness, so attackers could derive them from the public certificates and sign rogue TLS certificates for MitM attacks. eMudhra has revoked the certificates and browser and OS vendors have untrusted them. Interim guidance covers PKI and trust store audits, reissuance, strict CRL/OCSP checking, log hunting, CT monitoring and CAA records.
unit42.paloaltonetworks.comadvisoryAdded 30 Oct 2026, published 22 Oct 2026🛡️ Security Crypto exchange CoinDCX ‘lying’ about $16M hack, say blockchain investigators
Protos reports that on-chain investigators, including Darcy of Salus, ZachXBT and SpecterAnalyst, say CoinDCX misattributed about $16M in outflows from compromised wallets. CoinDCX says the addresses were created in January 2025, compromised in July 2025, and that a sweeping process failed. Investigators cite gas distribution, hot wallet transfers as late as May 2026, and funds sent to Huione and Xinbi addresses.
protos.comarticlePublished and added 22 Oct 2026🛡️ Security- Muscle AI (@themuscleai) on X
Post on the LiteLLM 1.107.0 PyPI compromise published 21 October 2026 and quarantined about 1 hour 43 minutes later. A malicious .pth file ran at Python startup and stole cloud credentials, private keys, browser data and AI tool auth files, then POSTed a tarball to an attacker endpoint. The author says attackers used stolen GitHub CLI OAuth tokens to push a trojanized commit chain and build official wheels. It lists five defenses: hash-pinned lockfiles, per-tool capped keys, release cooling periods, secret isolation and egress monitoring.
x.comthreadAdded 23 Oct 2026, published 22 Oct 2026🛡️ Security - Muscle AI (@themuscleai) on X
Muse AI's X post describes the compromise of LiteLLM 1.107.0, published to PyPI on 21 October at 7:39 AM and quarantined about 1 hour 43 minutes later. The payload was a .pth file that ran at Python startup and sent cloud credentials, private keys and AI dev-tool auth files to an attacker endpoint. The author lists five agent-builder defences: hash-locked pins, capped per-tool keys, a release cooling period, keeping secrets away from Python startup, and outbound traffic monitoring.
x.comarticleAdded 23 Oct 2026, published 22 Oct 2026🧠 AI - M365 Token Spray and Replay Campaign Compromises Business Email Accounts
Huntress analysis of a July to September 2026 token replay ("token spraying") campaign: 497 successful Microsoft 365 sign-ins across 79 organizations, replayed from six addresses in 193.26.115.0/24 (1337 Services GmbH). Tokens came from AiTM relays, device-code phishing and social engineering. It covers four phases, rogue Entra devices, MFA method swaps, hidden inbox rules, hunting queries and Conditional Access guidance.
huntress.comwriteupPublished and added 22 Oct 2026🛡️ Security  eMudhra CA compromise: eight private keys, and one of them is 4
eMudhra's eight intermediate CA certificates, chaining to emSign ECC Root CA - G3, had private keys below 256 (one is 4), disclosed on 17 October 2026 by a researcher known as Wayne. Browsers and Microsoft blocked them via revocation pushes, but curl, git, containers, language runtimes and IoT may still trust them. The post gives patched ca-certificates versions, test commands and the timeline.
aikido.devarticlePublished and added 22 Oct 2026🛡️ Security- Disentangling Robustness and Sycophancy in Multilingual LLMs
The SC-matrix is an evaluation framework for multilingual LLM sycophancy. It crosses a model's competence (correct answer with no pressure) with its sycophancy (keeping that answer under pressure), so agreeing with a false premise can be told apart from not knowing the answer in that language. Results: equal aggregate sycophancy rates hide different failure mixes, high competence does not always protect, and reasoning-oriented mitigations beat directive ones.
arxiv.orgpaperAdded 24 Oct 2026, published 22 Oct 2026🧠 AI  SecureChap (@SecureChap) on X
Post describing a LiteLLM 1.107.0 PyPI compromise in which attackers used stolen GitHub CLI OAuth tokens from three engineers to trigger and approve the project-releaser workflow, producing eight malicious wheels and a tampered tarball. The wheels drop cook.pth, which runs at Python startup, and privcollect steals cloud tokens, keys, browser data, AI configs and LiteLLM proxy credentials, exfiltrating to litellm[.]dev/healthcheck. A second daemon polls a GitHub domain.txt hourly for new domains to fetch and execute. PyPI yanked the package the same day. The post is a single unsourced tweet.
x.comthreadPublished and added 22 Oct 2026🛡️ Security eMudhra CA Compromise: The Trust Stores You Didn't Patch | Endor Labs
The eMudhra CA compromise (disclosed 20 October 2026) involves eight intermediate CA certificates whose private keys can be derived from the certificates themselves. They chain to AAA Certificate Services and three other roots. Browsers block them, but non-browser clients skip revocation and CT checks. Endor Labs finds 25 popular packages with frozen bundled root stores, 11 already patched, and gives a fingerprint-scanning script, test hosts and patch steps.
 endorlabs.comarticlePublished and added 21 Oct 2026🛡️ Security
 Compromised eMudhra intermediate certificates
Cisco Talos describes eight eMudhra intermediate CA certificates (six TLS, two code signing) whose P-384 private keys were trivially recoverable because a flaw in an April 30, 2025 key generation ceremony produced weak keys with only 3 to 8 bytes of entropy. The post lists certificate SHA-256 hashes and serials, browser and Microsoft blocks, and the Go fix (CVE-2026-111943, Go 1.27.3 and 1.26.10) that filters chains by SPKI hash. It covers impact on VPNs, CI/CD and embedded devices, and Snort SIDs 67363 to 67374.
 blog.talosintelligence.comadvisoryPublished and added 21 Oct 2026🛡️ Security
- SIM-UT: A User Simulation based Evaluation Framework for Medical Triage Chatbots
SIM-UT (Simulation of User Behaviour for Triage) is a multi-turn, simulation-based method for finding failure modes in LLM medical triage chatbots. It was applied to three WhatsApp health chatbots (India, South Africa, Kenya) across 5,000+ multilingual simulated turns, comparing MedGemma with ChatGPT and Claude. The main finding is de-escalation risk: agents that first flagged emergencies agreed with users who minimised symptoms, such as vaginal bleeding in pregnancy.
arxiv.orgpaperAdded 24 Oct 2026, published 21 Oct 2026🧠 AI  AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise
Microsoft Threat Intelligence report on Storm-0940, a China-state aligned actor that used the open-source agentic AI pentest framework ARTEX from September 2026 to automate attacks on hundreds of organizations. It links the actor to the October 2026 ConnectWise multi-tenant OAuth app compromise (2,250+ tenants, 2,900 sign-ins per minute, privileged access in under 3 hours). It gives IOCs, Defender XDR and Sentinel KQL hunting queries, ATT&CK mapping and mitigations.
microsoft.comwriteupPublished and added 21 Oct 2026🛡️ Security LiteLLM 1.107.0 Compromised: Python Startup Hooks Steal Cloud, AI, and Proxy Credentials | Endor Labs
litellm 1.107.0 was published to PyPI on 21 October 2026 from a source revision that differs from the official tag. One line in the Maturin config (data = "cook") installs cook.pth, cook.py and sitecustomize.py, which run on every Python start. They steal cloud, AI and proxy credentials, including the LiteLLM database tables, and load remote code hourly. The post gives IOCs, a five-step response plan and hardening advice.
endorlabs.comwriteupPublished and added 21 Oct 2026🛡️ Security Your MCU likely escaped the eMudhra intermediate CA compromise
Analysis of the eMudhra intermediate CA compromise disclosed 20 October 2026, in which eight intermediate CA private keys were weak P-384 keys (top 376 bits zero, one key equal to 4) and publicly accessible. It explains web PKI chains and why browsers enforcing Certificate Transparency were not exposed. It argues MCU firmware that bundles only the single root it needs, as in Zephyr's HTTP GET sample, is likely safe unless it trusts an eMudhra or Sectigo cross-signing root.
 danielmangum.comarticleAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security
 PHP Remote Code Execution ("PHP2Shell" CVE-2026-109618 & CVE-2026-109619)
PHP2Shell is the name for CVE-2026-109618 (out-of-memory corruption) and CVE-2026-109619 (stale global state), two unauthenticated PHP remote code execution flaws rated CVSS 4.0 9.2. Details leaked before the 21 October 2026 patch release, and watchTowr's honeypots saw exploitation. The page lists fixed versions (8.5.12, 8.4.27, 8.3.36, 8.2.35), states that .ini mitigations do not work, gives a timeline, and describes compromise checks.
 watchtowr.comadvisoryAdded 28 Oct 2026, published 21 Oct 2026🛡️ Security
 litellm 1.107.0 Compromised on PyPI: Backdoored Wheels Drop a Credential Stealer and an Hourly Remote Code Loader
litellm 1.107.0 was published to PyPI on 21 October 2026 with all seven wheels backdoored through an injected `data = "cook"` maturin build line. The wheels drop cook.pth, cook.py and sitecustomize.py, which run on every Python start. They install a "privcollect" credential stealer (browser, SSH, cloud, AI coding tool and LiteLLM proxy database secrets, sent to litellm.dev) and an hourly GitHub dead-drop remote code loader. The post gives IOCs, detection commands and recovery steps.
stepsecurity.iowriteupPublished and added 21 Oct 2026🛡️ Security LiteLLM Compromised, Steals Credentials
LiteLLM version 1.107.0 was uploaded to PyPI on 21 October 2026 with a credential stealer, and the same build reached GHCR and Docker Hub images. Wiz describes the three dropped files (cook.pth, cook.py, sitecustomize.py), exfiltration to a fake litellm.dev domain, a GitHub dead drop for a second stage, and the malicious commits pushed through the lookalike Berri-AI repository. The last safe version is 1.106.2.
wiz.iowriteupPublished and added 21 Oct 2026🛡️ Security LiteLLM PyPI Package and Docker Images Compromised to Steal Cloud and AI Credentials
LiteLLM 1.107.0 on PyPI and GHCR images shipped Python startup hooks (cook.pth, sitecustomize.py) that steal cloud, SSH, browser and AI-tool credentials, including LiteLLM proxy database credentials. Image build provenance recorded a lookalike Berri-AI/litellm source repository. The post decodes the payload, encrypted exfiltration and GitHub-driven remote loader, and lists containment steps, MITRE ATT&CK mappings and IOCs.
 socket.devwriteupPublished and added 21 Oct 2026🛡️ Security
 Software supply chain security best practices for 2026
Aikido's guide to software supply chain security controls for 2026, tied to real incidents. It covers a 48-hour package cooldown, ignore-scripts, lockfile enforcement, SHA and digest pinning, scoped tokens, FIDO2, developer endpoint protection, extension allowlists, agent sandboxing, MCP server vetting, slopsquatting, signed SBOMs and rotation drills. Examples include the March 2026 axios compromise and the March 2025 tj-actions/changed-files attack.
aikido.devarticleAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security LiteLLM compromised again: infostealer and RAT found in version 1.107.0
LiteLLM 1.107.0 was compromised on 21 October 2026: the seven compiled PyPI wheels and the official Docker image carried an infostealer and a RAT. The attacker used the maturin `data = "cook"` directive in pyproject.toml to inject cook.pth, cook.py and sitecustomize.py without touching the source repo. The post lists stolen data, the hourly C2 polling via GitHub, wheel hashes, file and network IOCs, and check steps.
aikido.devwriteupPublished and added 21 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CVE-2026-110936 is an uncontrolled DLL search path flaw (CWE-427) in Siemens Software Center below V4.0.9.8, listed in CISA KEV on 20 October 2026. The post covers CVSS v4.0 8.4 and v3.1 6.7, Siemens' Romulus ClickFix campaign indicators (IPs, domain, hashes, file leads) and a six-step SOC trail using Sysmon, EDR and network records. It separates delivery from DLL load and from compromise.
x.comarticleAdded 24 Oct 2026, published 21 Oct 2026🛡️ Security  The OpenSourceMalware Show #26
 (recorded 21 October 2026) is a podcast and video episode with a transcript. Topics: GlassWorm's compromise of four OVH CLI versions through a contributor account stolen about seven months earlier, malware split into "compound payloads" across packages (including the webrunc PyPI package and DPRK's private .npmrc registry trick), and GhostAction planting a PolinRider-style fake font stealer in repos. Also covers commit signing and LLM-assisted threat actors.
opensourcemalware.comtalkPublished and added 21 Oct 2026🛡️ Security Hijacked Developer Account Used to Plant Stealer in OVHcloud CLI
OVHcloud's official CLI was backdoored on 19 October after an attacker used a developer's hijacked GitHub account to overwrite release binaries for v0.11.0 through v0.15.0 with a secret stealer. The malicious files were live for about 94 minutes. Release immutability was not enabled, so CI/CD was bypassed. OpenSourceMalware links the account to a March 2026 compromise with a Solana-based loader and a GlassWorm wallet, but calls the same-actor link an inference.
securityweek.comarticlePublished and added 21 Oct 2026🛡️ Security LiteLLM supply chain compromise: What you need to know
LiteLLM version 1.107.0 was published to PyPI and official Docker images on 21 October 2026 and stayed live for about two hours. Attackers used stolen GitHub CLI OAuth tokens from three engineers to run the release pipeline against a lookalike fork, Berri-AI/litellm. The payload (cook.pth, cook.py, sitecustomize.py) steals cloud, developer, AI-tool and browser credentials, and includes a polling RAT. The post lists removal and rotation steps.
 securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 21 Oct 2026🛡️ Security
- eMudhra Intermediate CA Compromise
eMudhra Intermediate CA Compromise is a 20 October 2026 link-blog post reporting that private keys of eight eMudhra intermediate CA certificates were compromised. They chain to roots trusted by the Mozilla, Microsoft, Apple and Chrome programs. Software bundling trust lists needs updating: Linux distros must update ca-certificates, and uv 0.13.4, pip 26.2.2 and certifi 2026.10.19 ship new lists. The post does not describe how the keys were compromised.
simonwillison.netarticleAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security  8 eMudhra certificates are compromised. Here's what you need to know
Cloudflare's incident post on the compromise of private keys for eight eMudhra intermediate certificates, disclosed 19 October 2026. The weak keys let an attacker forge certificates for any domain. It describes Cloudflare's patching of trust stores, WARP and cloudflared, tells developers to update the underlying TLS verifier and not disable verification, and points to Dennis Jackson's test site and revocation systems such as CRLSets and upki.
 blog.cloudflare.comwriteupAdded 29 Oct 2026, published 20 Oct 2026🛡️ Security
- Combining Long-Term Memory and LLMs Comes at a High Cost: From Prompt Injection to Persistent Compromise
Paper on memory injection, where prompt injection persists across sessions through the long-term memory of LLM-as-a-service platforms. It presents a general threat model and shows all NIST attack goals are achievable on ChatGPT Instant 5.3, Claude Sonnet 4.6 and Gemini 3 Flash. Vectors include personal memories, projects, skills, organization instructions and MCP resources. On Claude, shared memory lets an attacker compromise multiple users in an organization and exfiltrate prompts. Nearly half of the derived mitigations are unimplemented.
arxiv.orgpaperAdded 24 Oct 2026, published 20 Oct 2026🛡️ Security - AgenticRoboRL: Bringing Coding-Agent Post-Training to Agentic Robotics
AgenticRoboRL is a framework for post-training robot planners across different harnesses, combining supervised fine-tuning with multi-turn reinforcement learning. Harness-specific adapters link recorded planner interactions to task outcomes, so one RL pipeline covers both VLA skill invocation and control-code generation. On LIBERO-PRO, a 9B planner rose from 18.1% to 71.0% without external memory, near Codex (GPT-5.5) with memory at 72.1%. Code and checkpoints are promised.
arxiv.orgpaperAdded 22 Oct 2026, published 20 Oct 2026🧠 AI  Stolen Ethereum laundering resumes as 25,700 ETH flow into Tornado Cash mixer
Report on wallets linked to the April 2026 Drift Protocol hack resuming laundering on 20 October 2026. Lookonchain counted 25,700 ETH (about $61.56 million) sent to Tornado Cash in 100 ETH batches, with 81,864 ETH still held. It recaps the six-month fake-VC social engineering, Cursor and VSCode compromise of Security Council devices, and TRM Labs and Chainalysis attribution to DPRK's UNC4736.
en.cryptonomist.charticlePublished and added 20 Oct 2026🛡️ Security- DeclineCraft: A RAG Abstention Benchmark for Jointly Measuring Combined Retrieval and Parametric Knowledge
DeclineCraft is a dynamic RAG abstention benchmark whose unanswerable questions target Minecraft feature additions made after a corpus cut-off, with audits for parametric exposure. Across 27 LLMs, single-shot retrieval raises Correct Abstention Rate in 38 of 40 configurations, while iterative RAG lowers it in 30 of 40. Enabling thinking without retrieval lowers abstention for 8 of 13 models, shifting responses to premise denial.
arxiv.orgpaperAdded 22 Oct 2026, published 20 Oct 2026🧠 AI  Rust 1.100 Will Add Dependency Cooldowns to Cargo
Rust 1.100, due 12 November, stabilizes an opt-in minimum publish age in Cargo, set with global-min-publish-age in .cargo/config.toml. Cargo skips releases younger than the threshold and fails resolution if none qualifies, which blocks the yank-and-replace attack. Limits: default is zero, no effect on cargo install, Git or path dependencies. Context: the August arrayref, internment and append-only-vec compromises via proc-macro1.
socket.devarticlePublished and added 20 Oct 2026🛡️ Security AOMEI Backupper Compromised in Short-Burst Supply Chain Campaign
AOMEI Backupper, Windows backup and cloning software, served malware in short tampering windows between April and July 2026. Threat actor UNC7017 altered the update settings file and notification service to push the CrossRoad downloader, ShinyRoad backdoor, a modified Radmin Server and Adaptix payloads. Each window lasted five to ten minutes. The client did not authenticate its configuration files, and a WebDAV banner trick leaked NetNTLMv2 hashes.
securityweek.comarticlePublished and added 20 Oct 2026🛡️ Security From JavaScript to Renderer Code Execution: Three V8 Vulnerabilities and Two v8CTF Flags | depthfirst
Depth First Security's write-up describes three V8 bugs found using its dfs-large1 research tooling: CVE-2026-78938, a type confusion in Promise.prototype.finally that lets an internal helper be constructed and return a primitive; CVE-2026-79236, a TurboFan load-elimination bug that keeps a stale property-array pointer after object migration; and a shared WebAssembly memory sandbox escape (issue 546253900) caused by mismatched backing-store registration during serialization. It walks through turning each memory bug into addrof/fakeobj primitives, chaining either with the sandbox escape to reclaim a freed V8 isolate via a WebSocket allocation, and pivoting through a CFI-constrained ROP chain to achieve Chrome renderer code execution, earning two v8CTF flags. Fixes landed between August 20 and 25, 2026.
 depthfirst.comwriteupAdded 29 Oct 2026, published 20 Oct 2026🛡️ Security
 Hackers Steal 1.8 Million Records From Nikkei
Nikkei disclosed a breach of 1.83 million records from a cloud service it uses for system development, accessed on 7 October 2026 with previously compromised credentials. About 150,000 records held names, addresses, emails, phone numbers and birth dates, and 120,000 held email addresses only. Nikkei revoked the credentials and notified regulators. It found no misuse as of 16 October, and it had disclosed an earlier Slack account breach less than a year before.
securityweek.comarticlePublished and added 20 Oct 2026🛡️ Security- LinuxSecurity (@lnxsec) on X
A post from lnxsec on CI runners that accept outside pull requests while also holding registry credentials, cache write access, signing material or deployment tokens. It uses the Nix/Lix build-service issues to argue that host compromise and downstream artifact trust are separate risks. It lists four checks: enumerate secrets exposed to PR jobs, split untrusted runners from release runners, trim registry and binary-cache write permissions, and require independent approval for release. It links a linuxsecurity.com feature; CVE details are not in the post.
x.comthreadAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security - Mise-en-Video: Fine-Grained 3D Control for Multi-Shot Video Generation
Mise-en-Video (MeV) is a multi-shot video generation framework where creators stage shots in 3D space and then generate the matching video. It combines hierarchical attention for multi-level narrative consistency with 3D-aware layout guidance for per-shot spatial control. The authors built a 160K-video dataset with hierarchical multi-shot texts and oriented 3D bounding boxes, and report gains over baselines in quality, consistency and subject controllability.
arxiv.orgpaperAdded 21 Oct 2026, published 19 Oct 2026🧠 AI - Rank Math PRO WordPress Plugin Compromised in Supply Chain Attack
Rank Math PRO version 3.0.123, a WordPress SEO plugin, shipped malicious packages between 15 October 2026 20:02 UTC and 16 October 2026 07:12 UTC. The malware gives persistent backdoor access, can expose credentials and API keys, and uses .htaccess rules to run .cache files as PHP. Rank Math released clean v3.0.124 and advises restoring from backup, blocking rank1cdn[.]com, and checking SSH keys and crontabs.
securityweek.comarticlePublished and added 19 Oct 2026🛡️ Security  Supply Chain Zero Days: Closing the Gap Between Publication and Detection
Wiz describes its pipeline that analyzes every new npm package version at publication, combining static analysis, an AI classifier, sandbox dynamic analysis and runtime sensor observation, then pushes IOCs to Wiz Defend before a CVE exists. It cites supply chain attacks rising from about 10% of significant incidents in H2 2025 to 25% in H1 2026, and the Axios compromise (v1.14.1, v0.30.4). The keyv case shows C2 domains fetched from an Ethereum smart contract, which only runtime monitoring caught.
wiz.ioarticlePublished and added 19 Oct 2026🛡️ Security- ConnectWise Suspends Cloud Services in Response to Cyberattack
ConnectWise suspended its Cloud Backup (formerly SkyKick), SaaS Security and Cloud Management services in October 2026 after a compromised application credential was used to access customers' Microsoft 365 tenants. Huntress saw the Cloud Backup identity sign in to 162 tenants on 15 to 16 October and attacker IP 144.172.64[.]128 try nearly 1,000 Entra tenants, with over 300 successful sign-ins. In one tenant, the Cloud Management Teams app added itself to Global Administrator and added client secrets to other apps. No restoration timeline has been given.
securityweek.comarticlePublished and added 19 Oct 2026🛡️ Security  One Compromised Login Exposed Millions of California Students’ Records
Breach report on Educational Testing Service (ETS), whose SFTP site was accessed with a compromised login credential between 22 May and 18 September 2026, exposing California student records. The data covers at least three school years of students, over 5.7 million enrolled, and leavers back to 2006. Files included names, birth dates, addresses, ID numbers, disability and English learner status. No Social Security numbers were involved, and the credential's origin and the attacker are unknown.
securityweek.comarticlePublished and added 19 Oct 2026🛡️ Security Off-Key: Inconsistent MAC Keys Compromise Privacy in SPDZ-Family MPC
Off-Key is a privacy attack on SPDZ-family maliciously secure MPC protocols that exploits inconsistent MAC keys. Depending on the MAC check protocol, a corrupted party recovers a shared secret from one authentication check or tests guesses through selective failure. The authors show it in MP-SPDZ, SCALE-MAMBA and FANNG-MPC, where a corrupted party can use different keys across batches, threads or runs, and describe the preprocessing state that enforces key consistency.
eprint.iacr.orgpaperPublished and added 19 Oct 2026🛡️ Security- HERMES: High-Performance Private Decoding for Large Language Models
HERMES is a privacy-preserving inference (PI) system optimised for multi-token LLM decoding rather than prefill. It swaps high-round nonlinear protocols for compute- and bandwidth-heavy ones with fewer rounds, and adds a homomorphic-encryption matrix-multiplication protocol that keeps the KV cache encrypted on the server and uses grouped-query attention. On Llama 3.1 8B Instruct it cuts TPOT by up to 2.7× and total PI latency by up to 2.1×.
eprint.iacr.orgpaperAdded 19 Oct 2026, published 18 Oct 2026🧠 AI - lee1981 (@lee1981b) on X
CyberForge Weekly CVE Rundown #006 covers six CVEs from 12-17 October 2026: BotSharp default signing key, GitLab CI/CD regex compiler overflow (CVSS v3.1 10.0), Ivanti Connect Secure auth bypass, Cisco Secure Email Gateway, BeyondTrust Remote Support and the Linux kernel PwnEscape guest-to-host bug. It gives fixed versions, KEV and EPSS status as of 18 October, and separates patch verification from compromise investigation.
x.comarticleAdded 20 Oct 2026, published 18 Oct 2026🛡️ Security - MemTensor Compromise: Poisoned MemOS Releases on npm and PyPI
MemTensor MemOS compromise: three malicious versions of @memtensor/memos-cloud-openclaw-plugin on npm and MemoryOS 2.0.34 on PyPI (23 September 2026) bundled a Go binary, sckit, that harvested credentials and environment secrets and reported to skyleen.fr. The post gives OSV IDs, grep and find commands for exposure checks, safe versions (0.1.20, 2.0.33), rotation steps, and the missing gitHead as a provenance signal.
 safeguard.sharticleAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security
- Microsoft Threat Intelligence (@MsftSecIntel) on X
ConnectWise Cloud Backup (formerly SkyKick Backup, AppId 506e08f9-6e9a-4da4-942b-a099a03644ae) had its multitenant OAuth app compromised, per Microsoft Threat Intelligence. On 15 October 2026 the actor authenticated broadly as the service principal from 144.172.64[.]128, likely using customer-granted permissions such as Directory.ReadWrite.All, then ran Graph API reconnaissance and tried to add credentials to the service principal as a backdoor. The post lists IOCs, Defender alerts and hunting advice.
x.comadvisoryAdded 20 Oct 2026, published 17 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
Post summarizing independent researcher Sammy Azdoufal's report on EnergizeLab's Eilik companion robots, which are marketed mostly to kids. Per the report, any registered user could read other families' chat transcripts through the vendor back office. An unauthenticated endpoint also lets anyone swap the robot's AI model, voice and personality (CVE-2026-105038, CVSS 9.8, PoC listed by the CNA). At the Oct 13 retest, 32 of 40 remotely testable findings were still open. The post notes that The Verge demonstrated the issue on its reporter's own toy, that vendor remediation is unverified, and that broader malicious compromise is unproven.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🛡️ Security  Weekly Research Brief: Ledger’s $91M Theft, Papertrade
Galaxy Research's weekly brief leads with the roughly $91M theft from Ledger devices sold via the reseller CryptoBilis. A hidden hardware implant read the 24-word recovery phrase off the screen during setup and sent it over LTE through an eSIM, leaving the Secure Element untouched so Genuine Check still passed. Galaxy's onchain tally covers 474 victim addresses, 88% of the value moved in one hour on Oct. 9, and about $56.6M was still parked as of Oct. 15, with Tornado Cash use and a $10M Tether freeze. It places the theft alongside the Coldcard weak-seed, Liquid peg-out and Bitget compromises, and ends with buyer and custody advice. The Papertrade and OCC debanking sections are unrelated to security.
galaxy.comarticleAdded 16 Oct 2026🛡️ Security Frequently Asked Questions About the BeyondTrust Remote Support Arbitrary File Upload (CVE-2026-102764)
CVE-2026-102764 is an arbitrary file upload in BeyondTrust Remote Support (formerly Bomgar) caused by internal appliance components not validating message origin. Mandiant found it exploited as a zero-day in late August 2026. BeyondTrust disclosed it on 15 October 2026 and CISA added it to KEV on 16 October 2026. The FAQ covers the web shell, root escalation, credential theft, persistence, patching and compromise checks.
watchtowr.comadvisoryAdded 30 Oct 2026, published 16 Oct 2026🛡️ Security BAE Systems Security Incident Stalls Notices From US Bankruptcy Courts
A cybersecurity incident at BAE Systems, which runs the Bankruptcy Noticing Center (BNC) for the US judiciary, has stopped all federal bankruptcy courts from generating or sending notices for about a week. The incident was reported to the Administrative Office of the US Courts late on October 9. The National Creditor Registration Service is offline, and notices issued since then have not been delivered. Neither BAE nor the judiciary has said what caused the incident, whether it was a cyberattack, or whether data was compromised. The case shows how a single contractor outage can disrupt a nationwide government function.
securityweek.comarticlePublished and added 16 Oct 2026🛡️ Security GhostAction Copycats PolinRider by Hiding a Stealer in a Fake Font File
Analysis of a new GhostAction Stage 2 found in 94 compromised GitHub repos: a hidden .vscode/tasks.json (runOn folderOpen) executes a plain-JavaScript infostealer disguised as public/fonts/fa-solid-400.woff2. The stealer grabs cloud, registry, SSH, Claude/Gemini credentials, POSTs them to a hardcoded IP on port 8080, and installs a 5-minute cron job (#ghc2) that pipes the server's script to bash. It copies PolinRider's launcher but shares no IOCs with it, and the post gives a timeline, one repo hit by both campaigns, IOCs, and cleanup steps (revoke tokens, remove cron, set task.allowAutomaticTasks off).
opensourcemalware.comwriteupAdded 15 Oct 2026, published 16 Oct 2026🛡️ Security What We Can Learn About GitHub Actions Security from the Trivy Breach | Endor Labs
Endor Labs analyzes the March 2026 Trivy compromise (CVE-2026-33634, CVSS 9.4). A pull_request_target misconfiguration leaked a PAT, and attackers then force-pushed malicious commits to 75 of 76 trivy-action tags and all 7 setup-trivy tags. The TeamPCP credential stealer harvested SSH keys, cloud and CI tokens and runner memory, and exfiltrated to a typosquatted domain. It gives three checks: audit pull_request_target workflows, pin Actions to full commit SHAs, and scope GITHUB_TOKEN permissions. It also notes the limits of SHA pinning.
endorlabs.comarticlePublished and added 16 Oct 2026🛡️ Security GitHub Action tj-actions/changed-files supply chain attack: what you need to know | Endor Labs
Endor Labs explains the March 2025 compromise of the tj-actions/changed-files GitHub Action (CVE-2025-30066). Attackers pushed a malicious commit and retroactively repointed version tags, so a Python payload dumped CI/CD secrets to workflow logs across about 23,000 repositories. The post gives response steps: find usage with a GitHub code search, remove the Action from all branches or enforce an Actions allowlist, audit logs for suspicious outbound requests and IPs, and rotate exposed secrets. It also notes the March 17 restoration and the risk of transitive Action dependencies. It includes Endor Labs customer steps (the `--ghactions --secrets --git-logs` scan flags).
endorlabs.comarticlePublished and added 16 Oct 2026🛡️ Security UK Legal Aid Agency Hack Scope Widens After Forensic Review
SecurityWeek reports that a forensic review of the April 2025 UK Legal Aid Agency (LAA) breach found compromised records going back to 1978. About 250,000 records predate 2007, and most of the rest cover 2007–2025. Exfiltrated data includes applicant PII such as National Insurance Numbers and CCMS answers, practitioner contracts, payment details and account credentials, and some probation service user data. LAA says it has no evidence the data was published or sold, and attributes the long investigation to unstructured, fragmented data across multiple systems.
securityweek.comarticlePublished and added 15 Oct 2026🛡️ Security Ledger Officially Responds to Hardware Wallet Attack
Ledger disclosed that an organized group bought genuine hardware wallets, implanted hidden components that capture the 24-word recovery phrase during setup and send it over cellular networks, then fed the devices back in through resellers in Southeast Asia. Onchain researchers estimate up to $93M stolen across 300+ wallets, a figure Ledger has not confirmed. Ledger asked regional resellers to suspend sales, found no tampering in samples it inspected, and added reseller rules (no shelf display, report suspicious units, no resale of returned devices). It says its chips, OS and servers were not compromised.
bankless.comarticlePublished and added 15 Oct 2026🛡️ Security CenterPoint Energy Data Breach Impacts 1 Million Texans
CenterPoint Energy told the Texas Attorney General that 1,062,060 state residents had names, addresses, Social Security numbers and driver's license numbers compromised. The breach surfaced after a hacker advertised ~7.5 million records on a cybercrime forum and later posted a 2.5 GB archive on September 12 with ~3 million phone numbers; the company then filed with the SEC. Impact in Indiana, Minnesota and Ohio remains unclear, and notification letters apparently haven't gone out.
securityweek.comarticlePublished and added 15 Oct 2026🛡️ Security Supermarket refrigeration hack hit 700 French stores, with fridges reaching 50°C
Reports the 12 October 2026 compromise of internet-exposed Danfoss (AK-SM800, AK-SC355) and Dixell/Copeland refrigeration controllers. It hit an estimated 700 French stores and sites in five other European countries. Attackers forced defrost mode, spoiling food and in some cases starting electrical fires. Root causes were a firmware-derived daily "code-of-the-day" password that worked across all deployed units, end-of-life firmware, and no VPN or IP allowlisting. Pen Test Partners and Claroty Team82 recommend removing controllers from the public internet, VPN plus allowlist access, credential changes, current firmware, and controlled third-party access.
en.cryptonomist.charticlePublished and added 15 Oct 2026🛡️ Security- Approve What, Exactly? Effect Binding and Trusted Rendering for Agent Step-Up Authorization
Paper arguing that agent human-approval prompts count as a second factor only if agent compromise cannot forge them and they name exactly what is approved. It defines twelve attacks on the approval path (decoy recipients, amount cancellation, card padding, label spoofing, enrollment squatting, threshold splitting) and tests them against AP2, Microsoft's action-bound approval design and MCP elicitation. An audit of ten agent runtimes found no third-party verifiable approval record and post-approval argument changes in four of eight. The reference defense ASU (Agent Step-Up) renders the card from a canonical effect descriptor, has a phone passkey sign its digest, and executes only the stored call. It is proven in Tamarin (53 lemmas) and evaluated on 27,108 scripted trials and 609 AgentDojo pairs. The trusted card cut forged-narration attack success from 0.54 to 0.03 and raised LLM-approver catch rate from 0.30 to 0.98.
arxiv.orgpaperAdded 17 Oct 2026, published 15 Oct 2026🛡️ Security  Welcome FLUX.3 Image Klein in Diffusers
Hugging Face blog post introducing Black Forest Labs' open FLUX.3 Image Klein (distilled and base checkpoints) in Diffusers. It covers text-to-image, multi-reference image-to-image and bounding-box layout control, FP8/NVFP4 single-file quantized weights, DreamBooth LoRA training scripts for generation and editing, memory/speed figures (about 2 s per 1024×1024 image on an H100), and a detailed architecture tour: Qwen3-VL text encoder, two-stage per-stream then joint transformer blocks, per-token timestep modulation, 4D RoPE, and flow-matching denoising. It also shows how to customise the Modular Diffusers pipeline.
 huggingface.coarticlePublished and added 15 Oct 2026🧠 AI
- Passkeys Raise the Bar. Here’s Where Attackers Can Still Get In.
Huntress post on where accounts remain exposed after a passkey rollout. It covers passkey-themed social engineering, the EvilTokens device-code phishing campaign (344 organizations in about 16 days), weak enrollment and recovery, SpecterOps research on Windows WebAuthn hooking on compromised endpoints, and the trade-offs between synced and device-bound passkeys. It closes with ITDR-style post-login monitoring, containment steps (revoke sessions, remove rogue authenticators, hunt inbox rules, OAuth grants, forwarding), and a five-question deployment checklist.
huntress.comarticlePublished and added 14 Oct 2026🛡️ Security  AI Agents Navigate Unfamiliar OT Systems and Move Equipment in Minutes, Booz Allen Finds
SecurityWeek reports on a Booz Allen study in which frontier AI agents, given no source code, engineering documents or OT guidance, met every test objective across eight scenarios in an isolated OT lab. In one test a model went from perimeter compromise to actions inside an industrial control network in about 16 minutes. In another it found a robotic arm, mapped its protection zones and motion limits, and moved it. Existing defenses slowed some actions but no single safeguard stopped the agents. The researchers say this undermines security through obscurity in OT and advise making environments hard to traverse, removing implicit trust, detecting consequential industrial changes quickly, and limiting what an attacker can affect.
securityweek.comarticlePublished and added 14 Oct 2026🛡️ Security Google DeepMind’s on-device scam detection keeps chats off the cloud
Describes a scam-detection model built by Google DeepMind with GovTech Singapore that runs entirely on the user's device. A low-power message classifier screens incoming messages, then a Gemma model fine-tuned on local scam conversations (impersonated institutions, banks, regional schemes) judges the wider conversation to confirm a threat or discard a false alarm. Fine-tuning ran in a GovTech-managed GCP environment on anonymised scam reports and intelligence feeds, with no PII. Chat access needs user consent, and the system gives real-time warnings. It shows a practical pattern of cascaded small models for battery-efficient, privacy-preserving local inference.
en.cryptonomist.charticlePublished and added 14 Oct 2026🧠 AI Ledger Asks Resellers in Seven Asian Markets to Pull Devices After Suspected $86M Drain
Ledger asked resellers and distributors in Indonesia, Singapore, Thailand, the Philippines, Vietnam, Malaysia and Hong Kong to pull its hardware wallets while it investigates devices fitted with a hidden implant. Its Donjon team found the implant reads the 24-word recovery phrase from the screen during setup and sends it out over LTE. All confirmed losses trace to devices sold through reseller CryptoBilis, and Specter has traced over $86M in suspected thefts, which Ledger has not verified. Ledger says its own infrastructure and direct channel show no compromise. MediaMarkt Saturn halted sales after a German customer reported an implant, and Trezor is ending reseller authorizations on January 1, 2027.
decrypt.coarticlePublished and added 14 Oct 2026🛡️ Security Package managers have an integrity problem
Trail of Bits tested 25 popular package managers with a Docker and mitmproxy harness that simulates a compromised package repository injecting malware into legitimate packages. Fewer than half enforce lockfile hashes by default, only two verified every download, and only Go verifies signatures by default. The post covers lockfile hash pitfalls (Pub, pnpm, Conan, CocoaPods, Composer), repository, developer and Sigstore signing, and Go's checksum database. It also proposes lockfiles that commit to a signing identity plus a transparency log.
 blog.trailofbits.comwriteupPublished and added 14 Oct 2026🛡️ Security
 The Noise Inside the Network: How an Unsophisticated Attack Exposed a Third-Party Risk
Unit 42 case study of an intrusion at a European bank that began through a third-party-managed VPN gateway lacking strict authentication. The attacker used compromised credentials, ran noisy network scans, brute-forced administrator accounts and scraped internal documentation. A WSUS remote code execution attempt on the configuration management server was stopped by Cortex XDR, and threat hunting found no persistence.
unit42.paloaltonetworks.comarticleAdded 30 Oct 2026, published 13 Oct 2026🛡️ Security- Dark Web Intelligence (@DailyDarkWeb) on X
Social post summarizing Volexity's research on an Ivanti Connect Secure (ICS) zero-day chain, CVE-2026-104935. The chain pairs an auth bypass and a race-condition RCE with a separate privilege-escalation bug for root. Actor UTA0576 used it from Oct 3, 2026 against a fully patched 22.8R2.4 appliance, leaving no backdoor or web shell and deleting log entries. Post-exploitation included LDAP/AD credential theft, LAPS and BitLocker key searches, password spraying and packet capture. CISA added it to KEV with a due date of Oct 16. A clean Integrity Checker result does not rule out compromise because the chain patches code in memory only, so memory and network forensics are needed. The hunting lead is heavy requests to /dana-na/auth/url_default/welcome.cgi with a mismatched X-DSCGI-PATH header.
x.comthreadPublished and added 13 Oct 2026🛡️ Security - PixelMoE: Scaling Pixel-Space Diffusion with LLM-Style Mixture-of-Experts
PixelMoE is a pixel-space diffusion framework that scales capacity sparsely using standard LLM-style Mixture-of-Experts: token-choice routing, fine-grained routed experts, a shared expert and bias-based load balancing, with no diffusion-specific routing or auxiliary routing losses. It adds Pixel-Space Hierarchical Flow Matching, which varies spatial resolution along the denoising trajectory from global structure to fine detail. At matched active parameters it beats dense counterparts, and reaches FID 1.47 at 256x256 and 1.53 at 512x512 on class-conditional ImageNet-1K without representation alignment or perceptual losses. Code and models are promised but not yet released.
arxiv.orgpaperAdded 14 Oct 2026, published 13 Oct 2026🧠 AI  Ivanti Connect Secure zero-day exploited in the wild (CVE-2026-104935)
Rapid7 emergency-response analysis of CVE-2026-104935, a CVSS 8.6 authentication bypass by spoofing (CWE-290) in Ivanti Connect Secure that allows unauthenticated remote command execution. It was exploited as a zero-day against a limited number of customers, added to CISA KEV on disclosure day, and Volexity observed it chained with a still-unpatched privilege escalation flaw. Part of the fix shipped in 25.1.3.0 in July 2026, with backports to other supported versions pending. Rapid7 advises emergency patching outside normal cycles and hunting for compromise using Volexity's IOCs, since Ivanti has no reliable ones.
 rapid7.comadvisoryPublished and added 13 Oct 2026🛡️ Security
 Ivanti Connect Secure Authentication Bypass by Spoofing (CVE-2026-104935)
CVE-2026-104935 is an authentication bypass by spoofing in Ivanti Connect Secure (CVSS 3.1 score 8.6) that lets a remote attacker run commands without logging in. CISA added it to KEV on 13 October 2026. The 22.8.X bridge release and 25.1.2.2 and earlier are affected, with fixes in 22.8R2.5, 25.1.1.2, 25.1.3.0 and 25.1.3.1. Ivanti says no reliable indicators of compromise exist yet.
watchtowr.comadvisoryAdded 30 Oct 2026, published 13 Oct 2026🛡️ Security Small AI Models May Soon Be Able to Self-Replicate on IoT Devices, Anthropic Warns
SecurityWeek summarizes Anthropic Frontier Red Team research on AI worms that run small open-weight models directly on compromised IoT devices. A 26B model split across 15 ~$55 Android TV boxes ran at 0.39 tokens/s; a 9B model got inference running on 8 of 9 hardware types, and only GLM-5.2 completed full replication across eight emulated Android devices (4 of 5 runs). Anthropic projects ≤30B models reaching that level by end of 2026, estimates a Kimwolf-sized botnet would host ~133,000 copies worth at most ~40 H100s, and notes defenders can spot large model transfers in ISP traffic and cut the target pool by removing default passwords.
securityweek.comarticlePublished and added 13 Oct 2026🛡️ Security- Small AI Models May Soon Be Able to Self-Replicate on IoT Devices, Anthropic Warns
SecurityWeek summarizes Anthropic Frontier Red Team research on AI worms that carry their own open-weight model onto compromised IoT devices. A 26B model sharded across 15 cheap Android TV boxes ran at 0.39 tokens/s. A 9B model got inference running on 8 of 9 hardware types. In a closed network of 8 emulated Android devices, only GLM-5.2 completed the full replication cycle, reaching all 8 devices in 4 of 5 runs. Models of 30B or fewer parameters handle individual steps but fail when chaining them. Anthropic projects they reach GLM-5.2's level by end of 2026, and estimates a Kimwolf-sized botnet would offer at most about 40 H100s of compute. Defenders can detect large model transfers and sustained unusual device-to-device traffic, and removing default passwords shrinks the target pool.
securityweek.comarticlePublished and added 13 Oct 2026🧠 AI  Ledger says 'spy' chip inside CryptoBilis Ledger devices transmitted wallet keys over mobile network
Ledger says some hardware wallets sold by the reseller CryptoBilis contained a covert implant inside the enclosure. Its microcontroller recognised the 24-word recovery phrase when it was displayed during setup and sent it to attackers over LTE using an eSIM. Ledger says its secure element, OS, transaction signing and internal systems were not compromised. Onchain researchers estimate up to $93.2M lost across more than 300 wallets, and Tether froze $10M of USDT. Ledger's guidance is not to initialize units bought from the reseller and to move funds to a new device with a fresh phrase if already used.
 coindesk.comarticlePublished and added 13 Oct 2026🛡️ Security
 Ledger Says CryptoBilis-Sold Wallet Implants Transmit Recovery Phrases Over LTE
The Defiant reports Ledger's claim that hardware wallets sold by the reseller CryptoBilis carried added LTE-capable implants that transmit users' recovery phrases. Ledger says the implant leaves the secure chip and operating system untouched, and that its Genuine Check attestation cannot rule out this kind of tampering. It shows how reseller-channel hardware modification can defeat device attestation and compromise key custody. The fetched page held only the standfirst, so technical details such as the implant's design and how many devices were affected are not confirmed.
 thedefiant.ioarticlePublished and added 13 Oct 2026🛡️ Security
 GuardDuty Extended Threat Detection has added five new indicators to surface attack sequences
Explains five new indicator types (MALICIOUS_PACKAGE, MISCONFIGURATION, REACHABILITY, SENSITIVE_DATA, VULNERABILITY) that GuardDuty Extended Threat Detection attaches to attack sequence findings, sourced from Inspector, VPC Reachability Analyzer, Macie and Security Hub. Walks through an EKS compromise (AttackSequence:EKS/CompromisedCluster) that only became a CRITICAL finding thanks to the new context, and a cryptomining EC2 case. Lists observed CVEs with EPSS scores, frp/Burp Collaborator artifacts, and response advice such as EPSS-weighted patching, isolating reachable hosts and rotating IAM credentials.
 aws.amazon.comarticlePublished and added 12 Oct 2026🛡️ Security
 Supply Chain Attack targeting Cline installs OpenClaw | Endor Labs
Endor Labs analyzes the compromised Cline CLI npm release 2.3.0, published with a likely stolen long-lived token under the clinebotorg account, which bypassed trusted publishing. Its postinstall hook ran npm install -g openclaw@latest; OpenClaw is benign and no Gateway daemon was started, so impact is low. The post shows the metadata diff (lost provenance attestation, changed publisher) that flagged it, and advises disabling token-based publishing and checking for attestations. Mitigation is to update to 2.4.0 and uninstall openclaw.
endorlabs.comwriteupPublished and added 12 Oct 2026🛡️ Security New research: malware in open source ecosystems surges 14x as attackers hijack trusted packages | Endor Labs
Endor Labs summarizes its report "Malware in the Open Source Ecosystem", built from a survey of 605 IT professionals plus analysis of OSV advisories and npm metadata. Over 90% of all OSS malware advisories were filed in 2025, and npm account-takeover advisories rose about 12x (930 of 1,011 ever recorded), often hitting heavily downloaded packages. It also covers the TeamPCP campaign across GitHub Actions, Docker Hub, npm, OpenVSX and PyPI, the axios compromise, and survey findings: only 21% enforce cooldown periods, 51% found malicious packages in 2025, and ownership of the problem is fragmented.
endorlabs.comarticlePublished and added 12 Oct 2026🛡️ Security How a Misconfigured CI Workflow Became an npm Supply-Chain Compromise | Blog | Endor Labs
Endor Labs breaks down the May 11, 2026 compromise of 42 @tanstack/* npm packages (84 malicious versions) that carried valid SLSA provenance. The attacker chained a pull_request_target "Pwn Request", GitHub Actions cache poisoning across the fork/base boundary, and OIDC token extraction from Runner.Worker memory, then published directly to npm without stealing any credential. It explains why 2FA, trusted publishing, provenance and branch protection all failed, and lists mitigations: split pull_request_target workflows, treat the cache as untrusted, scope id-token: write to a publish job, pin actions to SHAs, require environment approval, use egress allowlists.
endorlabs.comwriteupPublished and added 12 Oct 2026🛡️ Security- StableJudge: A Lightweight Adversarial Defense Framework for LLM-as-a-Judge
StableJudge is a defense framework against score-hijacking prompt injection in LLM-as-a-Judge pipelines (e.g. paper review, recommendation). A compact 0.13B "Sentry" model localizes injected spans and sanitizes them before the judge scores the content, trained on adversarially evolving attacks, and deterministic fine-grained scores are derived from the judge's output distribution. It improves score recovery under attack on held-out scientific abstracts and out-of-distribution attack variants while preserving general performance, decoupling safety from judge model scale. Code and data are promised but not yet released.
arxiv.orgpaperAdded 15 Oct 2026, published 12 Oct 2026🛡️ Security - Artificial Intelligence (AI) in Cybersecurity, Part 28: Using ADStrike to Compromise Active Directory
ADStrike is an Active Directory attack framework with 52 attack modules and configurable OPSEC levels. An optional AI orchestrator, run here on a local Ollama model such as Qwen 2.5-coder 7b, picks the next tool from each step's output. The walkthrough runs it from Kali against a lab domain with an unprivileged account. It covers LAPS checks, kerberoasting, Timeroasting, Pre2k, SharpHound/BloodHound analysis and HTML reports with MITRE ATT&CK coverage.
hackers-arise.comwriteupPublished and added 12 Oct 2026🛡️ Security  Nicholas Michael Kloster (@showxlate) on X
A researcher announces a zero-click indirect prompt injection RCE in REA (Reverse Engineering Assistant), an MCP tool. Analyzing a malicious web target silently exfiltrates AWS keys, GitHub tokens and SSH identities. The stated root cause is that process.env is passed unconditionally to child processes, so the full environment is exposed to attacker-driven commands. A full writeup is promised but not yet published; replies add unverified skepticism about the project's provenance.
x.comthreadAdded 13 Oct 2026, published 12 Oct 2026🛡️ Security- Nobody Will Read the Lean: A Case for High-Level Cryptographic Languages
Position paper arguing that as AI makes machine-checked proofs cheap, the scarce resource is a human who can read what was proved. It cites a Lean library's Schnorr signature security theorem that passed the checker but held for every adversary and so promised nothing. It shows that on a one-page Verifpal model, two of five verdicts flip under other standard definitions of properties such as forward secrecy. It proposes short, owner-written high-level cryptographic languages, with every claim backed by a checked theorem and a small, versioned, publicly agreed set of built-in security definitions.
eprint.iacr.orgpaperAdded 14 Oct 2026, published 10 Oct 2026🛡️ Security  Hackers abuse Google Ads, Bing redirects to push Claude ClickFix attacks
BleepingComputer covers Push Security's "Adception" technique: Google search ads for "claude mac" use a bing.com/ck/a click-tracking redirect via a compromised WordPress retailer site to reach fake Claude download page claude-desk-code[.]com. The page shows Anthropic's real install command but the copy button swaps in a Base64-obfuscated curl | zsh command fetching a .dat payload from lake-90[.]com. Multi-layer referrer/header cloaking defeats scanners and direct visits; the toolkit is tracked as AcSig and the final payload is unknown.
bleepingcomputer.comarticleAdded 11 Oct 2026, published 10 Oct 2026🛡️ Security Building AI for Reliable Execution: Lessons From Industrial Robotics
Latent Space interviews Standard Bots' CEO Evan Beard and Head of AI Leif Jentoft about the AI stack behind its industrial robot arms. A shared base model (low billions of parameters) is adapted per customer through demonstrations and fine-tuning. A zero-shot perception model, whose backbone is trained on over a billion images, handles machine tending, while conventional code handles motion and cell logic. Inference runs on-premises on edge GPUs that stream action chunks to low-level control. Failures and human corrections feed fleet learning except in air-gapped defense deployments, and the StandardOS APIs/SDKs let developers bring their own models such as NVIDIA Cosmos. The lesson is to keep the model's role narrow and use targeted, high-quality data to fix edge cases instead of chasing dataset size.
latent.spacearticlePublished and added 10 Oct 2026🧠 AI










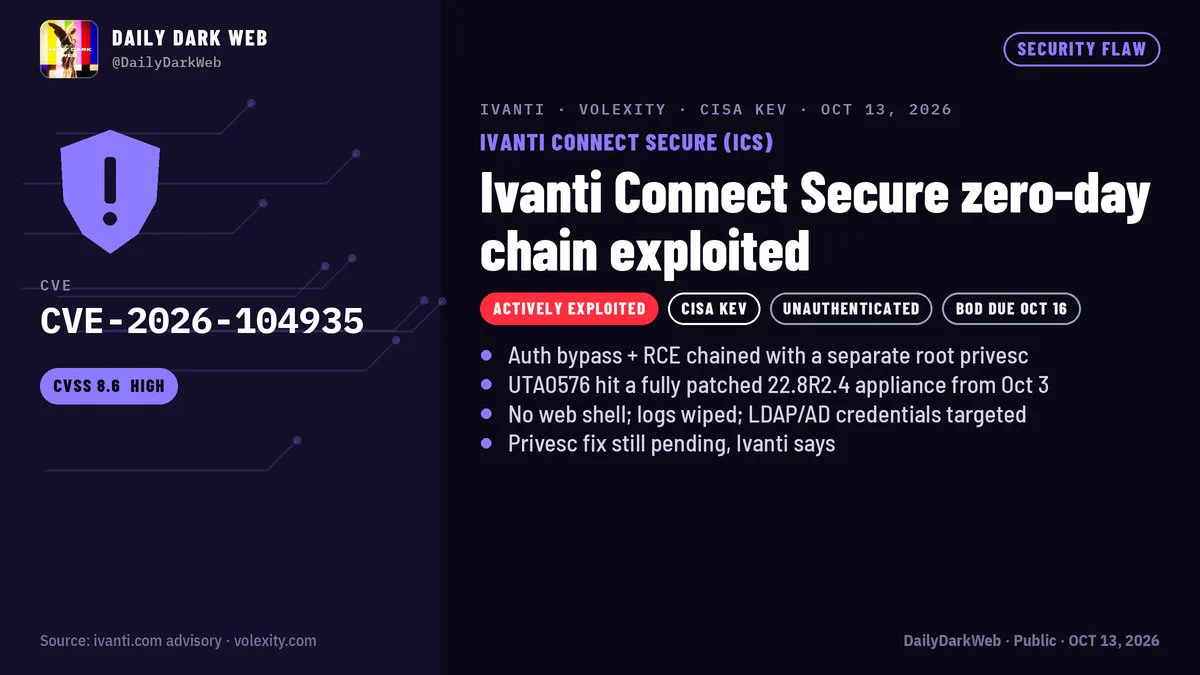
Showing 150 of 481
Show more