 “Black October” for AI Developer Platforms
Wiz Research links October 2026 breaches at AI developer platforms (Fireworks, OpenCode, Warp, Zeabur, Railway and others) to stolen environment-variable credentials for AI access. It details two enterprise AWS Bedrock keys abused after vendor breaches: about 800k and 1.7 million calls, over $100k in list-price usage. It profiles two LLM resale operations, "momo" and "Xingjiabi", that tested the keys.
 wiz.iowriteupAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
 20 security issues found in Xiaomi devices
Oversecured's write-up of 20 vulnerabilities in Xiaomi apps and system components, reported to Xiaomi between 25 and 30 April 2023. Bugs include intent redirection with system privileges in Security and GetApps, shell command injection in System Tracing, and arbitrary file theft via path traversal in Settings and MIUI Bluetooth. Each has a PoC. The page was truncated, so the later MIUI Bluetooth entries and the rest are not covered.
 oversecured.comwriteupAdded 29 Oct 2026🛡️ Security
 Disclosure of 7 Android and Google Pixel vulnerabilities
Oversecured discloses seven Android vulnerabilities, two of them Pixel-specific, all reported to Google and fixed except one low-severity WebView case. They are the Camera geolocation leak (CVE-2024-0017), a VPN bypass list change (CVE-2023-21383), a Bluetooth permission check flaw (CVE-2024-34719), the WorkSource parcel mismatch (CVE-2023-20963, exploited in the wild by the Pinduoduo app), Device Admin HTML injection (CVE-2021-0600) and a ContentProvider.openFile() caller-context bypass (CVE-2023-21292). Each has root cause and PoC code.
oversecured.comwriteupAdded 29 Oct 2026🛡️ Security The Rise of Agentic Attacks: What They Look Like, and Where They're Headed
Wiz research on intrusions where AI agents do the hands-on attacker work. It reviews public cases (ARTEX against South Korean banks and the ConnectWise compromise, Hermes at Thailand's Ministry of Finance, JPCERT/CC, CrowdStrike, DIVD) and three Wiz-investigated attacks. It distills fingerprints: machine-paced iteration, embedded natural-language reasoning, self-correcting scripts, checklist enumeration, noisy lateral movement, probe-before-payload habits and self-named scratch files. It also covers attribution, scale and defense implications.
wiz.iowriteupPublished and added 29 Oct 2026🛡️ Security Qwenputer: A functioning, deterministic RISC-V CPU inside Qwen3.5
Qwenputer is a stock Qwen3.5 4B with a 32-bit RISC-V CPU (RV32IM plus Zba and a bignum unit) compiled directly into added layers, with no training. Gated DeltaNet states act as exact RAM via gate 1, beta 1 and one-hot keys. It scores 97.5 to 100% on DeepMind arithmetic sets, and 100% on NUPA long-integer arithmetic. It also has an experimental in-model filesystem. The checkpoint is 18.8 GB and needs the RvChat driver.
 divagr.comwriteupPublished and added 29 Oct 2026🧠 AI
- Field Notes: Reconstructing an Attacker’s Workflow
Field note from dfir.ch on PowerShell scripts an attacker left on disk during an incident: a file-watching command runner using Invoke-Expression, a fake Windows credential prompt that validates passwords via Start-Process and logs them in cleartext, AD computer enumeration with WMI access testing, and SMB share discovery via NetShareEnum. It notes where script labels overstate what they prove and lists hunting strings for Event IDs 4104, 4103, 4688 and Sysmon 1.
 dfir.chwriteupAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security
 Profiling TorchNeuron (Part 1): System-level profiling on AWS Trainium.
Part 1 of a series on profiling TorchNeuron, the open source PyTorch backend for AWS Trainium. It shows how to configure torch.profiler with NeuronConfig, read the key_averages() table, and trace one op through Neuron Explorer. Three RMSNorm variants are compared: naive eager (2.355 ms device time), torch.rms_norm (403 μs) and torch.compile (375 μs).
 huggingface.cowriteupPublished and added 21 Oct 2026🧠 AI
 LiteLLM Compromised, Steals Credentials
LiteLLM version 1.107.0 was uploaded to PyPI on 21 October 2026 with a credential stealer, and the same build reached GHCR and Docker Hub images. Wiz describes the three dropped files (cook.pth, cook.py, sitecustomize.py), exfiltration to a fake litellm.dev domain, a GitHub dead drop for a second stage, and the malicious commits pushed through the lookalike Berri-AI repository. The last safe version is 1.106.2.
wiz.iowriteupPublished and added 21 Oct 2026🛡️ Security LiteLLM 1.107.0 PyPI Wheel Contains a Credential Stealer and Persistent Python Backdoor
LiteLLM 1.107.0 macOS x86-64 PyPI wheel analyzed by OpenSourceMalware contains three injected files (cook.pth, cook.py, sitecustomize.py) that run on every Python start. The payload, called privcollect, steals browser, SSH, cloud, CI/CD and AI-tool credentials, then uploads an AES/RSA-encrypted bundle to www.litellm.dev/healthcheck. A forked loader also fetches domain.txt from GitHub and executes /codepy hourly. The post lists IOCs, hashes and remediation steps.
 opensourcemalware.comwriteupPublished and added 21 Oct 2026🛡️ Security
 LiteLLM compromised again: infostealer and RAT found in version 1.107.0
LiteLLM 1.107.0 was compromised on 21 October 2026: the seven compiled PyPI wheels and the official Docker image carried an infostealer and a RAT. The attacker used the maturin `data = "cook"` directive in pyproject.toml to inject cook.pth, cook.py and sitecustomize.py without touching the source repo. The post lists stolen data, the hourly C2 polling via GitHub, wheel hashes, file and network IOCs, and check steps.
 aikido.devwriteupPublished and added 21 Oct 2026🛡️ Security
 CVE-2026-106173 Deep-Dive: FortiSIEM gRPC Path Traversal File Write RCE
CVE-2026-106173 is an unauthenticated arbitrary file write in the FortiSIEM phQueryMaster gRPC service on tcp/27918, advised by Fortinet on 13 October 2026. The SendQueryResult handler concatenates an attacker-controlled query-id into a path, and a null byte in the header removes the server-added filename suffix. Overwriting /opt/charting/redishb.sh, run every 60 seconds by cron, gives root-level code execution. IOCs are file timestamps.
 horizon3.aiwriteupAdded 29 Oct 2026, published 20 Oct 2026🛡️ Security
 Plex vulnerabilities being exploited in the wild to drop a cryptominer
Honeypot writeup of in-the-wild exploitation of Plex Media Server through the Plex2Shell chain (CVE-2026-96652, -96654, -96655, -96656) in October 2026. Attackers from 45.194.92.222, 91.92.40.202 and 176.65.139.228 used SSRF-style timeline/subscribe requests and downloaded a Docker-named dropper and an XMRig miner from 217.60.194.116. Includes file hashes, a later-seen proxyware sample (myawesomeproxy), lab pcaps for signatures and links to sandbox reports.
 boredhackerblog.infowriteupAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security
 GhostAction Copycats PolinRider by Hiding a Stealer in a Fake Font File
Analysis of a new GhostAction Stage 2 found in 94 compromised GitHub repos: a hidden .vscode/tasks.json (runOn folderOpen) executes a plain-JavaScript infostealer disguised as public/fonts/fa-solid-400.woff2. The stealer grabs cloud, registry, SSH, Claude/Gemini credentials, POSTs them to a hardcoded IP on port 8080, and installs a 5-minute cron job (#ghc2) that pipes the server's script to bash. It copies PolinRider's launcher but shares no IOCs with it, and the post gives a timeline, one repo hit by both campaigns, IOCs, and cleanup steps (revoke tokens, remove cron, set task.allowAutomaticTasks off).
opensourcemalware.comwriteupAdded 15 Oct 2026, published 16 Oct 2026🛡️ Security Investigating Ephemeral Supply Chain Tampering
GTIG and Mandiant report on UNC7017, which tampered with AOMEI update servers in five to ten minute windows between April and July 2026. Edited down_html.ini and Notifycfg.ini files delivered the CROSSROAD downloader and SHINYROAD PocketPy backdoor, plus Adaptix C2 and WebDAV NTLM coercion. The post covers infrastructure shifts, YARA rules, IOCs, and vendor and SOC guidance on point-in-time triage failures.
 cloud.google.comwriteupAdded 29 Oct 2026, published 15 Oct 2026🛡️ Security
 Jev as a judge: How counterfeit policy steers Jev
Datadog Security Labs tests TypeSafe AI's Jev decision model as a prompt-injection detector and as the judge behind LangChain's tool-risk gating. On four public datasets Jev had 99.66% precision and 82.90% recall. A prepended "counterfeit policy" that redefines the attack categories cut recall by over 79 points. In a LangChain scenario, a user-editable profile field lowered the mean is_risky score from 0.893 to 0.290, below the 0.5 block threshold. Plain prompt injection did not move the score.
 securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 15 Oct 2026🛡️ Security
 Artificial Intelligence (AI) in Cybersecurity, Part 29: Creating Isolated Autonomous Agents for Hacking with NemoClaw
Hackers-Arise tutorial on NVIDIA's open-source NemoClaw, which runs OpenClaw (and Hermes or LangChain Deep Agents) inside OpenShell sandboxes. OpenShell provides kernel-level isolation and declarative YAML policies for files, credentials and network access. It covers OpenClaw's risks (543 tracked CVEs, 40,000+ exposed instances), an OpenClaw vs NemoClaw comparison, the caveat that sandbox escapes and core-logic zero-days remain possible, and a Docker/Node.js install via the nemoclaw.sh wizard with TUI testing. It also cites the Cisco AI Defense plus OpenShell case study, in which an agent that does security patching was protected against a simulated exfiltration attempt.
 hackers-arise.comwriteupPublished and added 14 Oct 2026🧠 AI
 Package managers have an integrity problem
Trail of Bits tested 25 popular package managers with a Docker and mitmproxy harness that simulates a compromised package repository injecting malware into legitimate packages. Fewer than half enforce lockfile hashes by default, only two verified every download, and only Go verifies signatures by default. The post covers lockfile hash pitfalls (Pub, pnpm, Conan, CocoaPods, Composer), repository, developer and Sigstore signing, and Go's checksum database. It also proposes lockfiles that commit to a signing identity plus a transparency log.
 blog.trailofbits.comwriteupPublished and added 14 Oct 2026🛡️ Security
 Visual Studio Copilot and SSMS Remote Code Execution (CVE-2026-103572)
CVE-2026-103572 is a remote code execution bug in Microsoft.VisualStudio.Copilot.Core.dll, shared by Visual Studio and SQL Server Management Studio. A trailing dot (for example `.mcp.json.`) bypasses the protected-filename check in EditsFunctionHandler.GetEditConfirmationTypeAsync, so a hijacked Copilot can rewrite its own MCP and settings files and run commands. The post covers path traversal and InstallationID leaks, indirect prompt injection demos, the October 2026 patch (GetFullPath), and a $0 bounty.
 embracethered.comwriteupAdded 29 Oct 2026, published 13 Oct 2026🛡️ Security
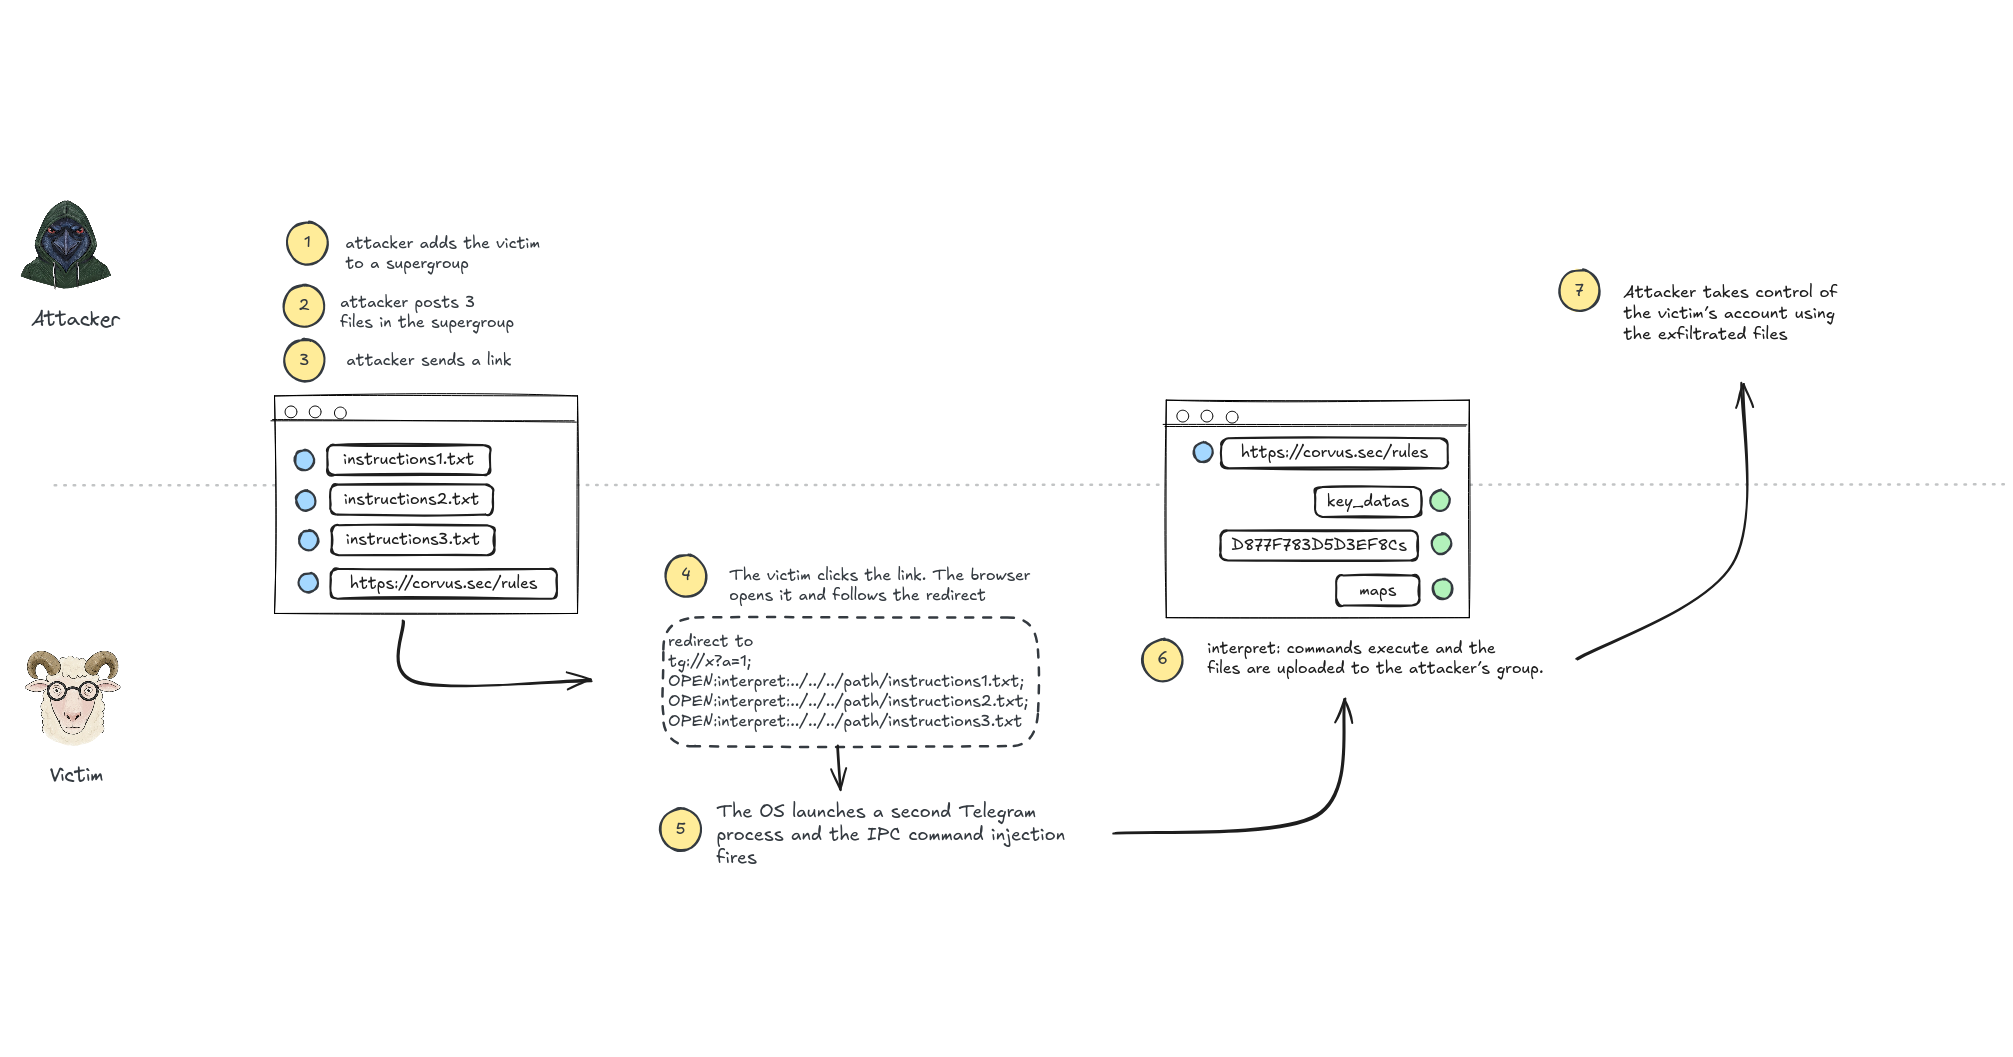 Telegram Desktop vulnerability allowed any user's file to be stolen
Writeup of a two-bug chain in Telegram Desktop: the single-instance local-socket IPC does not escape the semicolon record separator, so a clicked tg:// link injects extra OPEN: commands, which reach the internal interpret: scheme (InterpretSendPath) that reads an arbitrary file and sends it to a chat with no authorization or confirmation. The author plants instruction files via auto-download in a group, then exfiltrates tdata/key_datas and session files (no local passcode means an empty-password KEK) to take over the account. Fixed in 7.2.9 by removing interpret: and escaping separators; the post lists mitigations such as a local passcode and restricting who can add you to groups.
 beaksec.github.iowriteupPublished and added 10 Oct 2026🛡️ Security
 tensorlake NPM package compromised with Shai Hulud worm
Aikido details a new Shai-Hulud worm wave that compromised the tensorlake npm package (v0.5.144, 100k+ lifetime installs) via a hijacked GitHub maintainer identity. The malware's preinstall script drops the Bun runtime to run an obfuscated payload that exfiltrates CI/cloud secrets, browser crypto-wallet extension data (via a bundled HackBrowserData binary), uses a blockchain dead-drop (an Ethereum contract queried via public RPC nodes) to resolve a fallback C2, and includes a GitHub-token-triggered dead-man's switch that wipes infected machines. The post includes full IOCs: file hashes, the C2 domain iseekaigogo[.]com, and the threat actor's wallet/contract addresses.
aikido.devwriteupPublished and added 8 Oct 2026🛡️ Security Tensorlake npm Package Compromised: A Worm With a Hostage Token That Wipes Your Machine If You Revoke It
StepSecurity details how tensorlake@0.5.144 was pushed to npm after malicious commits landed directly on the tensorlakeai/tensorlake GitHub repo's main branch under a maintainer's identity, carrying a valid npm provenance attestation despite being malicious. The preinstall hook downloads Bun to run an obfuscated payload that steals GitHub/npm tokens, cloud and Vault/Kubernetes secrets, SSH keys, browser logins, and AI-tool configs (Claude, Cursor, Windsurf), then self-propagates by republishing stolen npm packages and committing persistence files (.claude/settings.json, .vscode/tasks.json) to reachable repos. A "hostage token" mechanism installs a gh-token-monitor service that runs a home-directory wipe if the stolen GitHub token is revoked before the monitor is removed, inverting the normal incident-response order.
 stepsecurity.iowriteupPublished and added 8 Oct 2026🛡️ Security
 Configuring your AI vulnerability harness, Part 2: The steering file
Part 2 of an AWS Security Blog series detailing the design of a "steering file" — a persistent instruction set (deployable as a Kiro steering file, Kiro skill, or Claude Code CLAUDE.md) that constrains an LLM performing vulnerability triage. It walks through five configuration sections: requiring structural/dataflow verification before reporting findings, replacing self-reported confidence with a weighted formula based on binary structural signals (e.g., 0.30 weight for confirmed taint flow), mapping infrastructure controls (AWS WAF, IAM) to severity multipliers with a 0.15 floor, incorporating CISA KEV and EPSS threat-intelligence boosts capped at +0.50, and a four-tier priority classification that suppresses low-confidence P3 findings. Validation against a 10-vulnerability test app showed the steered model eliminated fabricated findings and correctly downgraded mitigated vulnerabilities while preserving full severity for a command injection reachable only via authenticated access.
 aws.amazon.comwriteupAdded 8 Oct 2026, published 7 Oct 2026🧠 AI
 Post-Exploitation Analysis & Artifacts – Citrix NetScaler CVE-2026-88771
watchTowr post-exploitation analysis of CVE-2026-88771, an unauthenticated log-poisoning command injection in Citrix NetScaler (advisory CTX697096). Sensors logged thousands of attempts: about 85% were OOB callbacks, the rest Sliver implants, a trojanized Dropbear SSH backdoor, a Perl stager with a PHP webshell, and SSH-key and secret-harvesting sprays. Includes artifacts to hunt (/var/tmp files, ns_helper, ns.conf edits) and IOC repo pointers.
 watchtowr.comwriteupAdded 30 Oct 2026, published 7 Oct 2026🛡️ Security
 CVE-2026-21589: Critical unauthenticated arbitrary file access in Atlassian products
Rapid7's analysis of CVE-2026-21589 (CVSSv4 9.3), a critical unauthenticated arbitrary file read vulnerability affecting Bitbucket, Confluence, Jira Software/Service Management, Bamboo, Crowd, Crucible, and Fisheye Data Center products. It summarizes watchTowr Labs' root-cause finding that double-colon (::) sequences can act as path separators in Atlassian's web-resource handling, enabling path traversal to read arbitrary files within the Tomcat web root — including crowd.properties credentials that can be chained to create a rogue jira-administrators account. The post provides emergency patching guidance, Atlassian's WAF/RewriteValve mitigations, log-hunting regex, and notes public Python PoC and Nuclei templates exist.
 rapid7.comwriteupPublished and added 7 Oct 2026🛡️ Security
 How to Investigate a GitHub Repo's Real History
Step-by-step guide to reconstructing the real history of a tampered GitHub repo using data the attacker can't forge: raw commit objects (git cat-file), GitHub's repository activity API and audit log, before/after SHA ancestry checks, and npm publish timestamps. Worked through a PolinRider case (nestjsx/nest-access-control) where a forged commit was force-pushed to master plus 22 branches in 38 seconds, with a malicious .vscode/tasks.json runOn folderOpen trigger. It also covers safe handling of untrusted clones and how to tell victim accounts from attacker accounts.
opensourcemalware.comwriteupPublished and added 6 Oct 2026🛡️ Security You Won’t Hear About These, Even In Myths (Atlassian Jira, Confluence (and more) Pre-Auth Arbitrary File Read CVE-2026-21589)
CVE-2026-21589 is a pre-auth arbitrary file read in Atlassian Jira, Confluence and Bitbucket, found by diffing atlassian-plugins-webresource 6.0.7 against 6.0.8. The Router's unescapeSlashes turns "::" into "/", so "..::" traversal reaches WEB-INF files through download/resources routes. Reading crowd.properties leaks Crowd app credentials, which allow creating an admin user.
 labs.watchtowr.comwriteupAdded 30 Oct 2026, published 6 Oct 2026🛡️ Security
- Password Cracking: Stealing SSH Credentials with PAM
Walks through a post-exploitation credential-harvesting technique on Linux: enabling password authentication in sshd_config, writing a pam_exec.so logging script, and inserting it into /etc/pam.d/sshd (or common-auth/password-auth) so every SSH login attempt is logged with username, password, and source host to a hidden log file. Also covers using each user's ~/.ssh/known_hosts to identify pivot targets for lateral movement during a pentest.
hackers-arise.comwriteupAdded 7 Oct 2026, published 6 Oct 2026🛡️ Security - Up a Creek Without a Command Line: Mapping an Akira Ransomware Attack | Huntress
Huntress researchers reconstruct an Akira ransomware attack timeline using forensic artifacts collected after the Huntress agent was installed post-compromise, including Windows Registry Shellbags, Event Logs, and Akira ransomware log files. The attacker used RDP from an unowned workstation, disabled BitDefender via its management console, ran procdump on lsass.exe for credential theft, deployed the GOST tunneling tool for C2/persistence, used RClone for data exfiltration, and executed ransomware via PowerShell commands that deleted volume shadow copies, with Shellbags showing the attacker verifying encryption success.
 huntress.comwriteupPublished and added 6 Oct 2026🛡️ Security
 GitHub Copilot CLI vulnerability: Cryptographic Context Injection steals developer secrets
Adversa AI demonstrates Cryptographic Context Injection (CCI) against GitHub Copilot CLI: a web page presents an "encrypted" payload the agent decrypts inside its own shell, during which it is tricked into reading local files (e.g. .env.prod) to build a fake decryption key, then exfiltrates those contents to an attacker endpoint via a follow-up fetch. The attack only succeeds against certain models in Copilot's auto-routed model pool (Microsoft's mai-code-1.1-flash ran it 50% of the time, while two GPT-5.6 models refused), meaning users have no visibility into which model handles a given session. GitHub's bug bounty team validated but declined to treat it as a vulnerability since the user explicitly invoked autopilot mode with full tool permissions.
 adversa.aiwriteupAdded 7 Oct 2026, published 6 Oct 2026🛡️ Security
 CITRIX 0-DAY EXPLOITS: CVE-2026–88771 & CVE-2026–88772 IN THE WILD
An incident-response style deep dive into active in-the-wild exploitation of Citrix NetScaler ADC/Gateway via CVE-2026-88771 (unauthenticated RCE through log-poisoning of ns_monuploadd_err.pl) and CVE-2026-88772 (DTLS memory overflow), part of 8 CVEs disclosed by Citrix on September 27, 2026. The author reverse-engineers the full post-exploitation toolkit dropped after root is obtained: SLAPSHOT (a Perl/Python loopback TCP tunneler/pivot), WHIPSHOT (a disguised PHP web shell served via fake CSS paths), the Platypus C2 agent, and a Perl "Pitboss" dropper script (with full decoded source and an embedded SHA-256-protected PHP web shell) that creates a rogue superuser, SUIDs /bin/sh, exfiltrates NetScaler config, and patches httpd.conf for persistence. It closes with extensive IOCs (C2 IPs, file hashes, paths, credentials) and patch guidance for affected NetScaler builds.
 theravenfile.comwriteupPublished and added 6 Oct 2026🛡️ Security
 Beyond valid credentials: How exposed AWS keys are tested for Amazon Bedrock access
Datadog Security Labs describes how attackers test stolen AWS credentials for Amazon Bedrock access. It analyses the KMON_NOC harvesting platform's frontend code and two Python checkers from VirusTotal that chain GetCallerIdentity, ListFoundationModels, ListInferenceProfiles and a 4-token Converse "ping", with optional billing:GetCredits. Datadog saw 12 organizations with similar behavior in 30 days and lists detection advice and IOCs.
securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 6 Oct 2026🛡️ Security- Quoting Felix Rieseberg
A quote from Anthropic's Felix Rieseberg explaining why Cowork (Anthropic's agentic coding/tool-use product) moved from running a local VM for tool-call execution to running both model inference and the VM sandbox entirely in the cloud. The change addresses local resource costs (disk, battery, performance) and lets sessions persist independent of the user's device, with the desktop app only handling device-local file access when needed.
 simonwillison.netwriteupAdded 6 Oct 2026, published 5 Oct 2026🧠 AI
 Active Supply Chain Attack: Malicious node-ipc Versions Published to npm
StepSecurity's AI Package Analyst detected three malicious node-ipc versions (9.1.6, 9.2.3, 12.0.1) published simultaneously on May 14, 2026 by a rogue/compromised maintainer account, injecting an 80KB obfuscated IIFE into the CommonJS bundle that harvests 90+ credential file categories (AWS, Azure, GCP, SSH, Kubernetes, GitHub, Claude AI/Kiro configs, Terraform, etc.) and exfiltrates them via HTTPS and raw DNS TXT queries to a typosquatted Azure-mimicking C2 domain. The writeup includes a full stage-by-stage technical teardown (daemonization, SHA-256 targeting gate on 12.0.1, custom base-16 nibble-reversed obfuscation, dual-channel exfiltration) plus file hashes, network IOCs, and remediation guidance for developers and CI/CD pipelines.
stepsecurity.iowriteupAdded 5 Oct 2026🛡️ Security MALFEX npm Malware Campaign: Three Payloads And An Adversary That Signs Their Work
Checkmarx's research team documents MALFEX, an npm supply-chain malware campaign run by a single operator ("Murizada") publishing since August 2023, with 12 packages (8 malicious), three still live as of late September/October 2026. The campaign delivers three distinct Windows payloads: Overlord RAT (a Go-based C2 that reads its server address from encrypted Solana blockchain transactions and uses process hollowing into TapiUnattend.exe), the movinlike Node.js stealer (targeting Discord, browser credentials, Telegram, and crypto wallets, exfiltrating via Discord webhook), and a long-running downloader hidden in function-flag's postinstall script. The writeup includes full IOCs, file hashes, host artifacts, detection commands, and remediation guidance for compromised Windows hosts.
 checkmarx.comwriteupAdded 7 Oct 2026, published 5 Oct 2026🛡️ Security
- How Huntress Detects and Responds to a ClickFix Attack
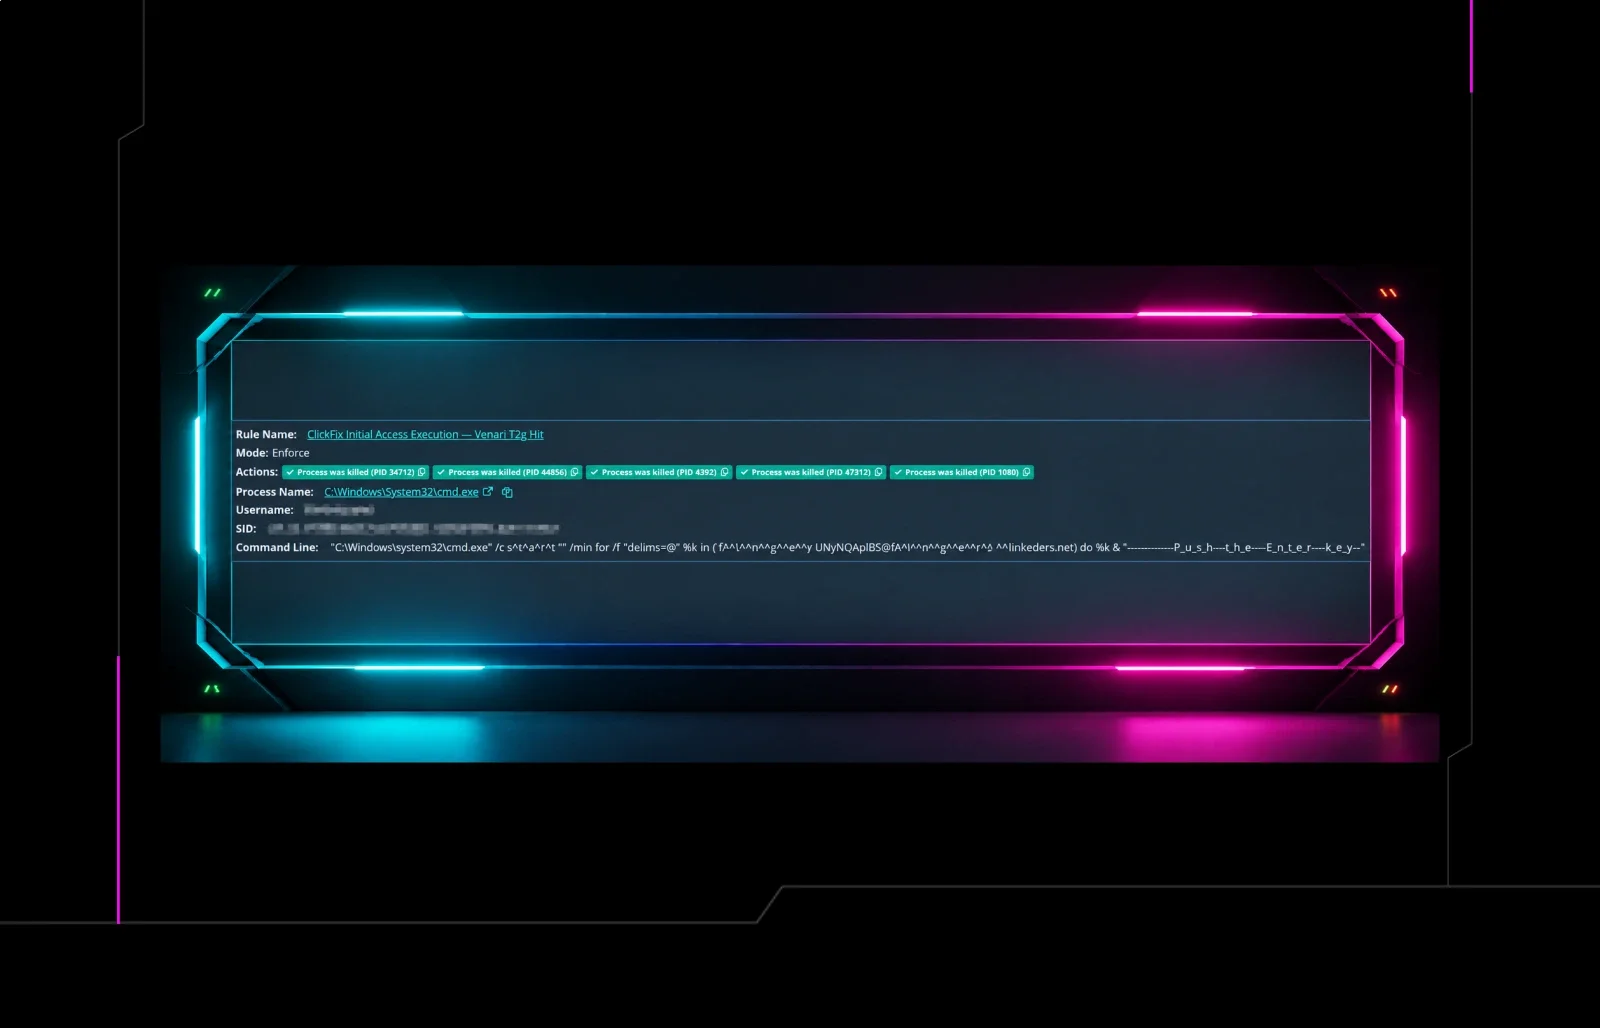
Huntress explains why endpoint security typically misses ClickFix (no file artifact to scan) and how its Attack Disruption engine detects it instead: matching the obfuscated command-line shape gated on the parent process always being explorer.exe for Windows+R/Run-dialog execution. The post walks through a real incident where a user pasted a caret-obfuscated finger.exe download cradle disguised with Unicode padding to hide 'push enter' social engineering text, killed in under 1.25 seconds across four spawned processes, and describes a fix for variants that use 'start' to detach the payload process from its killed parent.
huntress.comwriteupPublished and added 5 Oct 2026🛡️ Security  Malicious Crypto Shell Packages Target RubyGems
OpenSourceMalware's analysis of over 40 typosquatted RubyGems packages (e.g. rubygems-btc-shell) published by a user calling themselves "Ghost Dev," targeting crypto/web3 developers. The packages ship a delayed-execution payload hidden in extconf.rb that evades sandboxes before either opening a reverse shell to 45.138.12.177:8090 or deploying a full theft kit (inject_proxy.py, _grab.py, a browser extension, and a rogue root CA) that MITMs TLS traffic to 28+ crypto exchanges, swaps withdrawal addresses, hijacks the clipboard, and harvests wallet files, seed phrases, and private keys. The writeup includes full IOCs, SHA-256 hashes, attacker wallet addresses, and C2 endpoints.
opensourcemalware.comwriteupPublished and added 5 Oct 2026🛡️ Security- Xray-core concealed a certificate verification bypass vulnerability
A security researcher's first-person disclosure describing a certificate verification bypass in Xray-core (a popular censorship-circumvention proxy): when its pinnedPeerCertSha256 option skips regular TLS verification, a MITM attacker can insert a leaf certificate anywhere in the certificate chain and have the custom pinning logic incorrectly validate it, effectively eliminating certificate verification. The writeup also documents how the vulnerability was silently fixed with a misleading "simplify the code" commit message and left undisclosed to users for nearly half a year until the reporter filed a GitHub Security Advisory.
 github.comwriteupAdded 5 Oct 2026, published 4 Oct 2026🛡️ Security
- Today I learned: Python's .start Files as a Persistence Mechanism
Explains PEP 829's new .start files in Python 3.15, which let a package register package.module:callable entries in site-packages that execute automatically every time an interpreter starts, before any user code runs. The author walks through a reproducible lab showing code execution via a .start file, contrasts it with the older executable-import .pth file technique it replaces, and gives forensic hunting commands (using python -S to avoid triggering the mechanism during investigation) to locate and audit .start files on disk.
dfir.chwriteupAdded 6 Oct 2026, published 4 Oct 2026🛡️ Security - The First 24 Hours: What Happens When Ransomware Lands
An hour-by-hour ransomware incident response playbook written by UnderDefense CEO Nazar Tymoshyk and published on Huntress's blog, covering confirmation, containment, exfiltration detection, backup/recovery pitfalls, and root-cause investigation in the first 24 hours of an attack. It draws on Mandiant's M-Trends 2026 report (14-day median dwell time, 22-second access-broker-to-ransomware handoff) and CISA's November 2025 Akira advisory (VPN without MFA as primary access vector, exfiltration via FileZilla, WinRAR, WinSCP, RClone, Mega and Ngrok, credential dumping with Mimikatz and LaZagne, PowerShell-based shadow copy deletion) alongside real UnderDefense engagement anecdotes.
huntress.comwriteupAdded 3 Oct 2026, published 2 Oct 2026🛡️ Security - Pentesting: Managing Compromised Machines with Platypus
Walkthrough of Platypus, an open-source C2-style host management platform (github.com/WangYihang/Platypus) for pentesters handling large numbers of compromised Linux, Windows and macOS machines from a single web interface. Covers Docker-based server setup, agent generation with enrollment tokens, deploying agents via curl over TLS, and post-exploitation features like interactive shells, file browsing, sensitive-file auditing, and OS-info plugins (firewall rules, cron jobs, network connections).
hackers-arise.comwriteupAdded 7 Oct 2026, published 2 Oct 2026🛡️ Security  SMTP is the key: BPFDoor and AVERAT hitting the network edge
Rapid7 details a new BPFDoor campaign targeting telecom and network-edge appliances (ShareTech, SpamSniper mail gateways) and a six-sample Linux RAT family dubbed AVERAT found on compromised Taiwanese CPE (Synology NAS, a NetKlass device, a Dahua DVR). The writeup reconstructs the Rapid7 BPFDoor controller's HTTP-tunneled trigger mechanism, a fileless ShareTech dropper that stages binaries as ntpdate/udevds and deletes them while processes keep running, a BPF Rekoobe variant that hides inside SMTP port-25 traffic, and AVERAT's RC4-derived config/C2 scheme — tying the infrastructure to the broader China-nexus ORB (Operational Relay Box) device pattern described in CISA/NCSC-UK advisory AA26-113A. It closes with detection guidance for unlinked/deleted process execution, dropper staging artifacts, and port-25 C2 callbacks, plus full IOC and ATT&CK tables.
rapid7.comwriteupAdded 7 Oct 2026, published 2 Oct 2026🛡️ Security- Field Notes: Reconstructing the Attacker's LSASS Dump
DFIR.ch field notes on an incident where attackers used Ricardo J. Ruiz's TrickDump tool to dump LSASS without creating a conventional minidump file, instead leaving lock.json, shock.json, barrel.json and a ZIP of randomly-named memory-region chunks. The authors reconstructed the dump with TrickDump's create_dump.py and parsed it with pypykatz, confirming the attacker actually recovered reusable Kerberos credential material rather than just detecting that LSASS was touched. Includes hunting guidance (Sysmon EID 10 process-access telemetry, SeDebugPrivilege enablement, multi-binary workflows) and notes TrickDump fails against LSASS protected by PPL.
dfir.chwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security  From SELECT to SYSADMIN with SQL Copilot (CVE-2026-65669)
Write-up of a BlueHat Asia 2026 talk on CVE-2026-65669, a critical SQL Server elevation of privilege in Copilot in SQL Server Management Studio. The read-only mode was only a regex classifier (LocalSqlExecutionAccessChecker) and was bypassed with DECLARE @p sysname='sp_executesql'; EXEC @p. The chain used indirect prompt injection through AGENTS.md and CONSTITUTION.md extended properties to take a db_owner to sysadmin, with data exfiltration via xp_dirtree and RestoreVerifyBackupFile.
embracethered.comwriteupAdded 29 Oct 2026, published 30 Sep 2026🛡️ Security China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor
Cisco Talos details UAT-11587, a China-nexus threat cluster targeting government, defense, and policy organizations across Taiwan, India, the Philippines, Cambodia, and other Asian countries with spear-phishing and a five-stage infection chain (HTA/WSF stagers, JScript decryptors, .NET BinaryFormatter/ActivitySurrogateSelector deserialization gadgets, and DLL sideloading via the signed GatherOsState.exe) to deploy a new Rust-compiled backdoor called Antino. Antino uses Microsoft Graph/Outlook/OneDrive as a dead-drop C2 channel instead of a traditional C2 server, supports shell/PowerShell execution, file transfer, shellcode loading with a sleep-mask evasion technique, and abuses the Windows Scripted Diagnostics framework for persistence; Talos also notes possible infrastructure overlap with Symantec's "Jewelbug" cluster and Arctic Wolf's UNC6384 reporting. Includes ClamAV/Snort coverage and IOCs.
 blog.talosintelligence.comwriteupAdded 7 Oct 2026, published 30 Sep 2026🛡️ Security
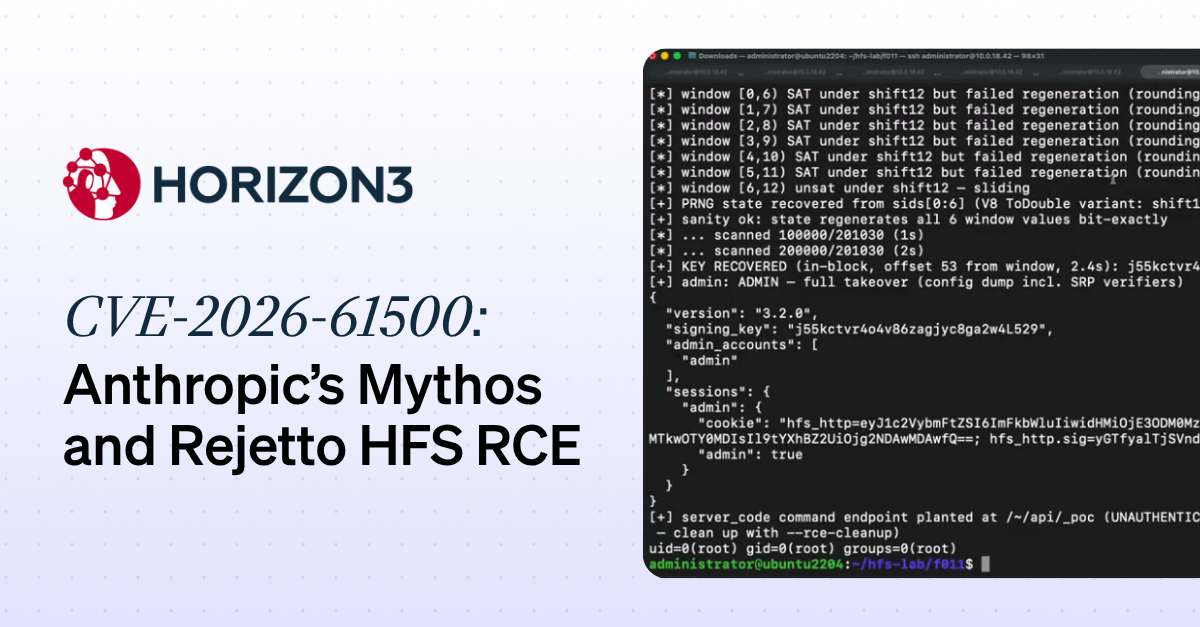 CVE-2026-61500: Rejetto HFS Session Forgery Vulnerability (found via Anthropic Mythos)
Horizon3.ai discloses CVE-2026-61500, a session-forgery vulnerability in Rejetto HTTP File Server (HFS) 3.x found using Anthropic's Mythos model. HFS seeds Koa's keygrip session-signing key with V8's insecure, invertible Math.random() PRNG and separately leaks raw Math.random() outputs through an unauthenticated login endpoint; by sampling a dozen leaked outputs and feeding them to the Z3 SMT solver, an attacker can recover the xorshift128+ internal state, step it backwards to the process-start signing key, and forge an admin session cookie that leads to remote code execution via HFS's built-in admin JavaScript execution feature. The piece walks through the full exploit chain and argues that Mythos independently chained the crypto weakness and the leak, built the Z3-based key-recovery solver, and produced a working PoC without additional prompting.
horizon3.aiwriteupAdded 7 Oct 2026, published 30 Sep 2026🛡️ Security- Determined Attacker Uploads Malicious Webshells to Parks and Rec Management Platform Servers
Huntress details a four-act intrusion against a shared parks-and-recreation management platform running on IIS, where an attacker first tried noisy unauthenticated exploits (IIS 8.3 tilde enumeration, WebDAV verb abuse, upload-handler bypasses) before simply registering a member account and uploading .aspx webshells via a member-file upload feature across three servers. The attacker enumerated hosts, extracted web.config/connection strings, hunted for cardholder data (Fortis/MXMerchant webhook logs, CVV/card-number strings), then escalated to timestomping, re-deploying known-filename webshells, and finally injecting an AI-generated PowerShell/JS dropper into a trojanized jQuery file to turn site visitors' browsers into WebRTC/WebSocket C2 clients (ririmochii/bubuneeko Cloudflare Workers infrastructure). Includes a zh-CN PowerShell user-agent string used for attribution and full command/IOC listings useful for detection engineering.
huntress.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security  Phishing Abuses RMM Tools for Persistent Access
Microsoft Defender Experts document a July 2026 phishing campaign that delivers a masqueraded but legitimately signed MSP360 RMM installer (v2.5.0.67) via meeting-invite, Zoom, Adobe, and DHL-themed lures hosted on both attacker infrastructure and legitimate cloud services (S3, Cloudflare R2, Dropbox, GitLab, Supabase). After UAC-elevated installation and service persistence, the RMM.Agent.exe service launches PowerShell to silently install a ConnectWise ScreenConnect client via msiexec, which the actor then uses via RunFile to drop credential-theft and reconnaissance tools disguised as Windows/Defender/Phone Link components. A separate July intrusion used FaronicsDeployAgent.exe the same way to deploy ScreenConnect, showing the technique is not MSP360-specific; Microsoft provides IOCs, hunting queries, and mitigation guidance (Application Control, AppLocker publisher rules, ASR rules) but does not attribute the activity.
 microsoft.comwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security
 Beyond source code: A path to the keys to the kingdom
Microsoft's DART team details an investigation into Storm-3068, a threat actor that escalated from a self-service password reset account takeover into full control of an organization's Azure DevOps environment, then weaponized a malicious pipeline to harvest kubeconfig files and gain access to Kubernetes clusters. The actor also deployed the Atera remote management agent and the Chisel tunneling tool to establish reverse tunnels and alternate remote access, and exfiltrated seven stolen kubeconfig files into a repository. The report lays out the attack chain, DART's response, and hardening recommendations around SSPR monitoring, phishing-resistant MFA, branch protection, and pipeline permission controls.
microsoft.comwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security OpenAI DevDay 2026 live blog
Simon Willison's live-blogged notes from OpenAI DevDay 2026 cover a raft of product launches (the "dots" personal agent, GPT-6.1 Sol, Ultrafast inference, ChatGPT Sites, GPT-Live), but the security-relevant core is the Codex Security session: OpenAI describes an internal "Defense Factory" security sprint that fixed 53 critical findings in a day, and launches a major Codex Security Cloud upgrade plus an open-source Codex Security CLI. The tool builds a security knowledge base, reads per-repo SECURITY.md threat-model files, runs a looping scanner, deduplicates findings (36% of their internal findings were duplicates), and can auto-generate patches/PRs validated by a "verify-fix" adversarial agent (1% rollback rate).
simonwillison.netwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security Star Blizzard refines phishing and malware delivery with the RedFlick technique
Microsoft details how Russian FSB-linked threat actor Star Blizzard evolved its phishing and malware delivery tradecraft throughout 2026, introducing a new technique dubbed "RedFlick" that uses scheduled tasks to deploy the CosmicPulse backdoor with only a single user interaction, down from the multi-step ClickFix chains used previously. The report covers the shift from targeted spear-phishing to large-scale phishing campaigns using accounts on compromised WordPress/CPanel websites, delivery chain variants (VHDX files, Control Panel applet (CPL) masquerading, steganography, PDF-embedded payloads), and the related DarkSword iOS backdoor, affecting 100+ organizations tied to Ukraine support. It includes IOCs, KQL hunting queries for Microsoft Defender/Sentinel, and mitigation guidance.
microsoft.comwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security- Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix
Huntress researchers document a campaign where attackers built a malicious ChatGPT Custom GPT ("Plus 5.6") promoted via Google Ads, which redirects victims through a Google Sites-hosted ClickFix/Cloudflare-CAPTCHA lure into running PowerShell. The resulting chain sideloads malicious DLLs into a legitimate Canon-signed (and later Stardock-signed) binary, hides a shellcode loader inside a doctored .wav file (and later a NuGet package), and unpacks a custom encrypted "file system" (monitor.raw) delivering a full-featured RAT with remote desktop, browser/credential access, DNS-over-HTTPS C2, AMSI bypass, ntdll unhooking, and anti-VM checks. Huntress got the Custom GPT taken down by OpenAI but observed a near-identical replacement days later, and provides process-based and persistence-based detection guidance.
huntress.comwriteupAdded 29 Sep 2026, published 28 Sep 2026🛡️ Security  PolinRider is A/B Testing its Way Past Your Detections
Opensourcemalware.com traces PolinRider, a DPRK-linked supply-chain malware delivered via a poisoned .vscode/tasks.json that autoruns an obfuscated payload disguised as a Font Awesome .woff2 file, through an 8-month infection of three real GitHub repos (Binary-Mindz org). Using GitHub's server-side activity log they reconstruct 853 force-pushes showing the operators A/B-testing multiple concurrent payload variants (400/500/900), rewriting commits to impersonate legitimate cleanup commits, hiding payloads inside eslint.config.mjs and prisma.config.ts, and using an Ethereum-wallet-based C2 dead-drop (NullReceiver). The post lists why common detection heuristics (filename search, whitespace padding, marker strings) fail against the new variants and gives working detections (file-type checks, folderOpen task grepping, activity-log force-push monitoring) plus full IOCs.
opensourcemalware.comwriteupPublished and added 26 Sep 2026🛡️ Security The Infostealer Incursion: How Stolen Credentials Breach Cloud, Code, and AI Environments
Wiz Research analyzed infostealer-harvested secrets (via its NordStellar integration) to map exactly which credentials malware families like Lumma, RedLine, and Vidar target across AWS, Azure, GCP, GitHub, GitLab, and AI platforms, and how those secrets translate into cloud account takeover. It gives concrete file paths and artifacts attackers hunt for (~/.aws/sso/cache OIDC tokens, Azure accessTokens.json, GCP credentials.db/access_tokens.db, GitHub gh hosts.yml and SSH keys, GitLab Runner config.toml, OpenAI/ChatGPT session cookies, and Claude Code's ~/.claude/.credentials.json OAuth tokens), plus stats: three malware families cause 85.7% of incidents, AWS/GCP account for 46%/13% of stolen secrets, GitHub ~10%, AI platforms ~5%. It also covers CI/CD-targeting infostealers (Miasma, TeamPCP) and session-cookie hijacking as an MFA bypass technique.
wiz.iowriteupAdded 27 Sep 2026, published 25 Sep 2026🛡️ Security Malicious Firefox Extension Poses as PDF Identity Verifier to Hijack Google Accounts
Socket's Threat Research team dissects a malicious Firefox extension (pdf-para-texto@extensao.local, "PDF Identity Verifier") that ships with no hardcoded malicious code — all attack logic is fetched as data into browser.storage.local after install via a lookalike domain (pdf.gusercontent.com), evading static store review. Once armed, it abuses Google's FedCM API to silently identify the victim, injects a live automation script into real accounts.google.com pages to drive an invisible account-takeover flow (bypassing password entry, forcing passkey challenges, dodging Google's bot detection, and forcing/capturing a password reset), while a webRequest listener steals the oauth_token session cookie from Set-Cookie headers — giving the attacker both a live session and a durable new password. The campaign targets Portuguese- and Spanish-speaking users starting September 2026 and includes full IOCs (domains, file hashes) and remediation steps.
 socket.devwriteupPublished and added 23 Sep 2026🛡️ Security
- OAuth Token Theft Through Microsoft's Front Door | Huntress
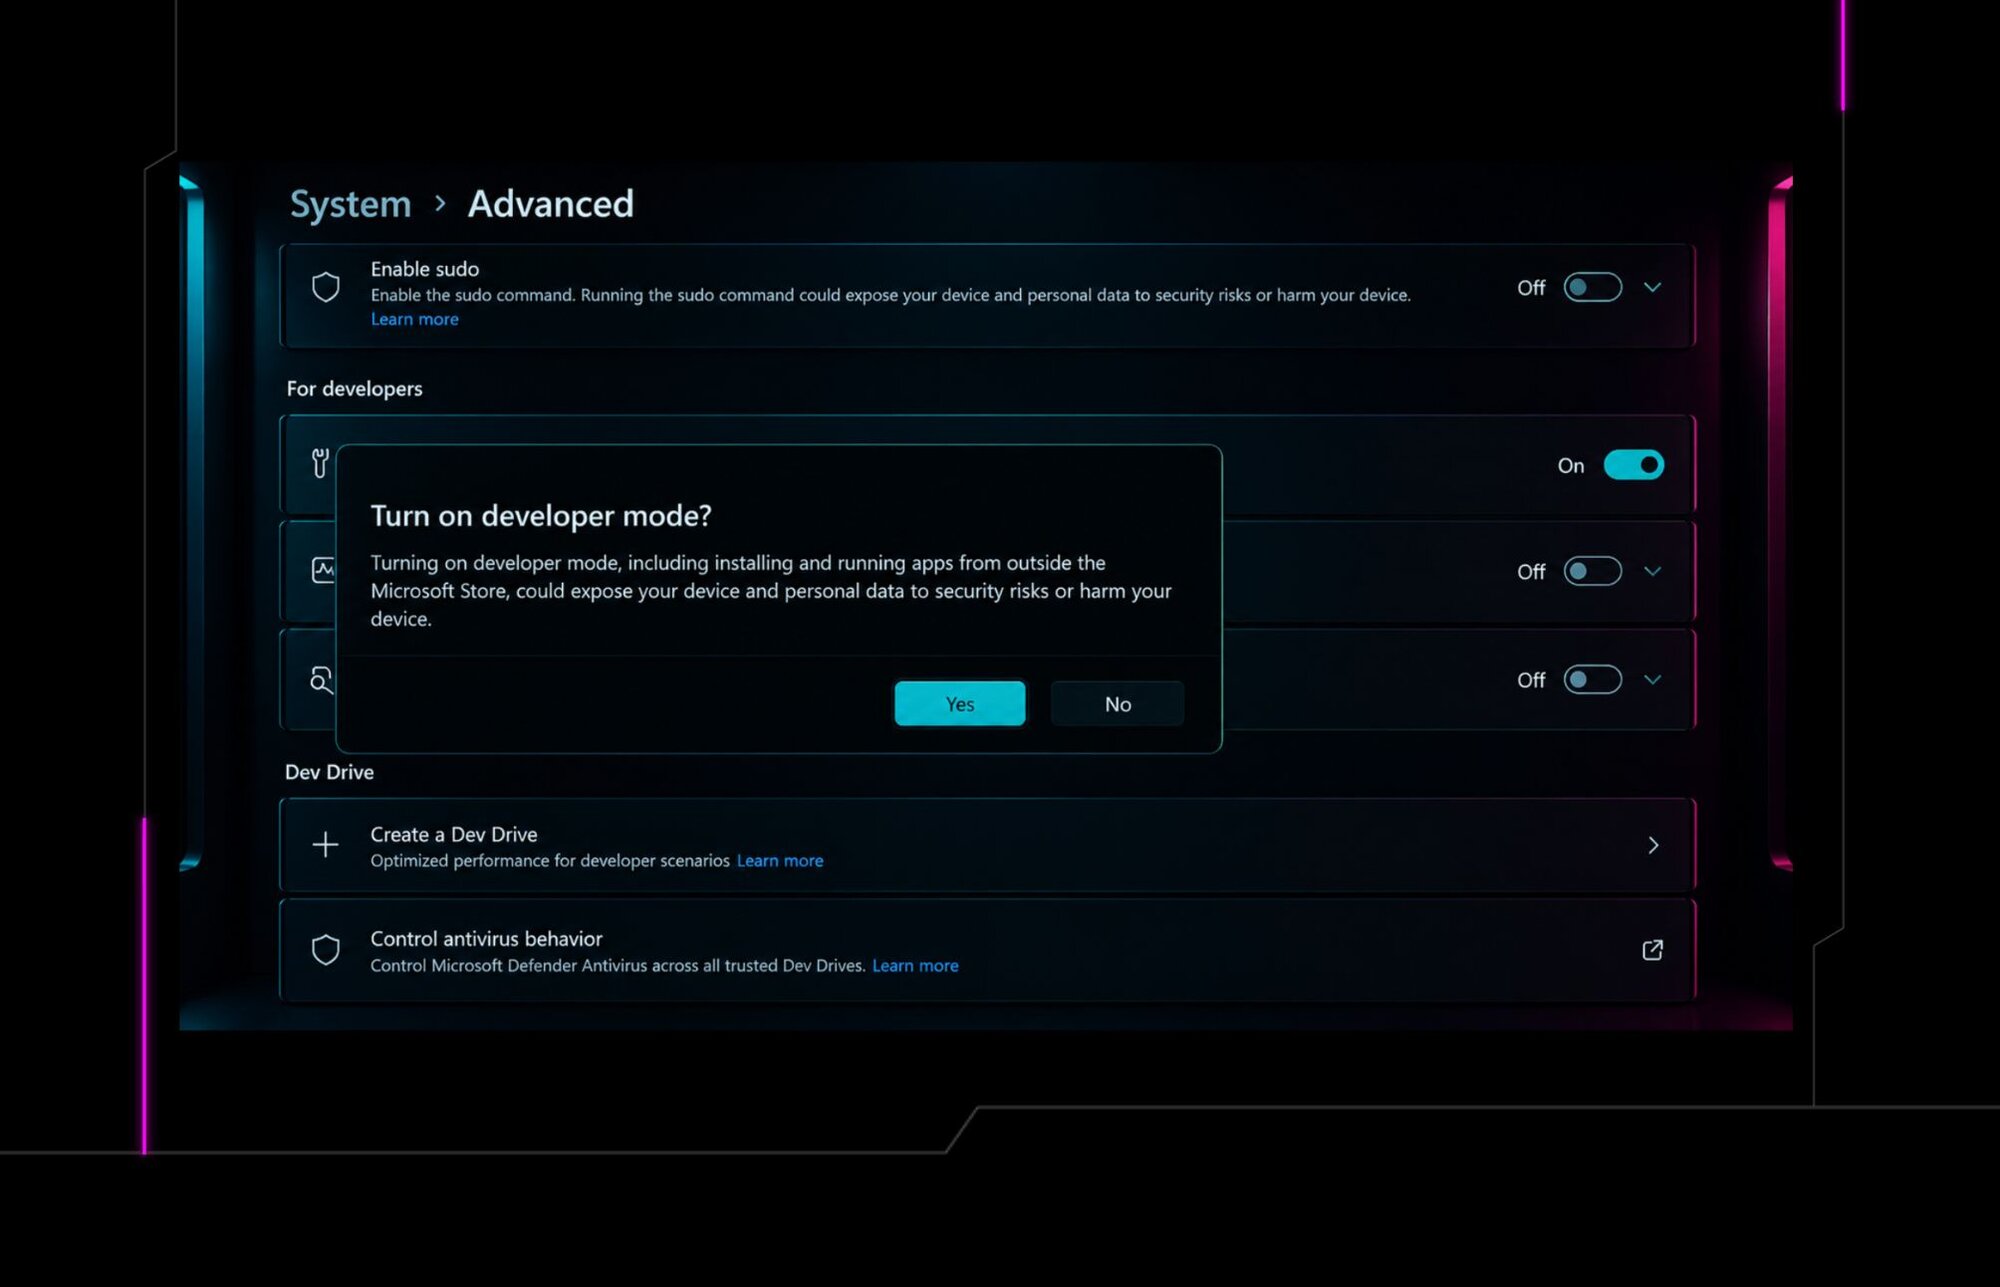
Huntress researcher Andrew Schwartz demonstrates a novel OAuth token-theft technique: a sideloaded AppX package registered via Add-AppxPackage -Register (requiring only Developer Mode, no admin beyond that toggle) can set ContentUriRules WindowsRuntimeAccess="all" so attacker-controlled JavaScript rendered inside the Microsoft-signed WWAHost.exe process gets full WinRT access, including the legacy WebAuthenticationBroker OAuth API. Using Microsoft Office's own client ID and the oob redirect URI, the attacker triggers a genuine login.microsoftonline.com/MFA dialog with no browser chrome, captures the auth code, and exchanges it for an access token plus a long-lived refresh token carrying the full Office delegated Graph scope set (mail, files, Teams, directory, AuditLog.Create) — validated end-to-end against a live Entra ID tenant with MFA and default Conditional Access. The post frames it as a class of vulnerable signed AppX host binaries sharing the same WinRT activation layer, and provides a Sigma rule keyed on the MSAppHost/3.0 EdgeHTML user agent reaching non-Microsoft destinations, plus Sysmon/Event ID and GPO-based mitigations (restricting Developer Mode, Conditional Access, shorter refresh-token lifetimes, CAE).
huntress.comwriteupPublished and added 23 Sep 2026🛡️ Security - DarkMe RAT: A VB6 APT Trojan Turned Conventional Infostealer
Huntress details a 2026 DarkMe RAT campaign that ditches the zero-days (CVE-2023-38831, CVE-2024-21412) previously used by the Water Hydra/EvilNum-linked group in favor of a plain phishing email delivering a disguised .pif file. The writeup reverse-engineers the full chain — msiexec pulling a wrapped MSI, a WSF stager, three obfuscated VB6 loader DLLs (Coconout.dll, Use.dll, Finalized.dll), a novel 329-app "inverted sandbox" gate, process hollowing into a signed clspack.exe, and Locked:// protocol-handler persistence — and corrects prior public reporting by showing the payload's "single-byte XOR" is actually a broken RC4 implementation. It closes with fresh C2 infrastructure (thatawful[.]boutique, port 7712), OSINT on delivery domains (including a related ClickFix/Efimer campaign), and concrete Sigma-style hunting rules and remediation steps.
huntress.comwriteupAdded 23 Sep 2026, published 22 Sep 2026🛡️ Security - The Tale of Two INC Ransom Notes: A Ransomware Timeline | Huntress
Huntress details a post-incident investigation into an INC ransomware attack that hit 175+ endpoints, reconstructed from surviving EDR telemetry and Windows event logs rather than live detection. The intrusion shows a 17-day gap between initial scheduled-task persistence and RDP lateral movement (possibly an initial access broker), and a second wave using AnyDesk, a BYOVD tool (hwau.exe loading the HwAudio kernel driver) to disable security controls, and Impacket's atexec.py to deploy INC ransomware. Attackers dropped two distinct ransom notes 53 minutes apart: a standard INC-README.txt and a detailed DATALEAK_PRESS_RELEASE.txt threatening to notify media, employees and partners with a full inventory of stolen files.
huntress.comwriteupAdded 22 Sep 2026, published 21 Sep 2026🛡️ Security - Compromised npm Packages in the AsyncAPI Namespace Deliver Miasma Botnet Loader
Socket's Threat Research Team details a supply-chain compromise of four @asyncapi npm packages (generator-helpers, generator-components, generator, specs) published via a poisoned source commit through GitHub Actions trusted publishing. The packages contain an obfuscated load-time (not install-hook) implant that spawns a detached Node.js process to fetch an IPFS-hosted, AES-256-GCM-encrypted loader delivering the "Miasma" botnet/tasking framework, which supports REST C2, multi-channel comms (Nostr, IPFS, Ethereum RPC, BitTorrent DHT), shell execution, file exfiltration, and systemd persistence. Includes full technical analysis, IOCs, hashes, and MITRE ATT&CK mapping.
socket.devwriteupAdded 21 Sep 2026🛡️ Security  Socket: Two Joyfill npm Beta Releases Compromised to Deliver DEV#POPPER Remote Access Trojan
Socket's research team found two beta releases of the @joyfill npm packages (@joyfill/layouts and @joyfill/components) contained an import-time JavaScript implant that resolves encrypted payloads through Tron, Aptos, and BNB Smart Chain transactions, ultimately dropping a 77KB Node.js remote-access trojan matching the DEV#POPPER family and sharing loader fingerprints with the PolinRider blockchain-loader campaign. The RAT establishes a Socket.IO C2 channel, executes arbitrary JS/shell commands, exfiltrates files and clipboard data, and persists by patching files inside VS Code, Cursor, Antigravity, Discord Desktop, GitHub Desktop, and the global npm CLI; a parallel detached-process branch fetches an additional bootstrap that can deploy a Python credential/browser-data stealer assessed as an OmniStealer variant. Because the implant fires on module load (not via npm lifecycle scripts), `--ignore-scripts` provides no protection, and the writeup includes full IOCs, blockchain addresses, C2 infrastructure, and MITRE ATT&CK mappings.
socket.devwriteupAdded 22 Sep 2026, published 20 Sep 2026🛡️ Security- Ready, Settra, Go: New Settra Ransomware Variant Deploys MeshAgent RMM
Huntress analysts detail two Settra ransomware incidents (July and September) observed in customer environments, documenting the threat actor's use of the MeshAgent RMM for persistence, BYOVD via the gdrv.sys driver, and anti-forensic techniques including Windows Event Log clearing, reagentc /disable, diskpart-based recovery partition removal, and cipher.exe free-space wiping. The post includes specific IOCs — C2 IPs 45.13.122[.]7 and 193.5.65[.]114, the recurring workstation name WIN-LIVFRVQFMKO, and the RESTORE_FILES.txt ransom note — supplementing prior public reporting from MoxFive and SOCRadar on this newer ransomware variant first seen in June.
huntress.comwriteupAdded 22 Sep 2026, published 17 Sep 2026🛡️ Security






Showing 60 of 204
Show more