 Agents Prompt People: Using Agents for Long-Horizon Financial Work
Latent Space podcast write-up of an AI Engineer New York interview with Aman Singh, lead AI Engineer at Arca, an AI-native wealth management firm. Arca runs agent tasks lasting up to ten days, uses a per-client memory system, and owns its harness, which routes tasks to models (mainly Claude) by internal benchmarks. Safety rules are deterministic, trading stays with human advisors, and a meta-agent uses advisor feedback and traces to improve the harness.
 latent.spacearticlePublished and added 31 Oct 2026🧠 AI
 Anthropic security breach exposed salaries and messages, not model weights
Anthropic security incident in which researchers from the startup Cathedral reached Anthropic's commercial, HR and IT systems through vulnerable third-party administrative applications. Exposed data included salaries, job offers, meeting transcripts and Slack messages; Anthropic says customer prompts, source code and model weights were not accessed. Anthropic cut access the same day and kept the apps disabled until vendors patched. The companies dispute whether Cathedral reported all its activity.
 en.cryptonomist.charticlePublished and added 30 Oct 2026🛡️ Security
 Rekt - News or Hype?
Rekt's "News or Hype?" compares four October 2026 AI headlines with their sources. These are Justin Drake's "bunker mode" ECDSA warning, Anthropic's Claude tracing NIST curve seeds to lrand48, OpenAI's agent spending Sepolia ETH from a default-mnemonic account, and Wiz's "AI uncovers" PHP RCE claim of 70% reach. It ends with four questions for checking claims.
 rekt.newsarticleAdded 30 Oct 2026🧠 AI
- Show HN: I Turned DOOM into a Transformer
Doomformer compiles integer neural networks into ZDoom maps that run in ViZDoom. Voodoo dolls do the arithmetic, and sector light levels and plane heights hold the values. Python reads every value back and compares it with a NumPy integer reference at tolerance 0. It runs MNIST (97.16 % on all 10,000 digits, every pass exact), small transformers, a learning perceptron and a SUBLEQ machine. It is about 23,000 times slower than NumPy on a small MLP.
 github.comrepoAdded 30 Oct 2026, published 29 Oct 2026🧠 AI
 world2vec: Mechanistic world models through latent dynamics learning
world2vec is a method for learning mechanistic world models from observations and actions alone, without reward information. Its latent dynamics reproduce the true system over long prediction horizons using at least one order of magnitude fewer parameters than DreamerV3, TD-MPC2 and LeWM. The authors report state-of-the-art control of continuous environments from pixels and accurate system identification across a benchmark of 71 attractors.
 arxiv.orgpaperAdded 31 Oct 2026, published 29 Oct 2026🧠 AI
- Efficient Scalable Oversight via Rewinding
Rewindable interactive proofs (RIPs) are a new model of relativizing interactive proofs for scalable oversight, in which a weak verifier can rewind an AI prover to an earlier saved state. The paper builds an RIP for computations robust to changes in a small fraction of oracle answers. The honest prover runs in linear time, the verifier runs in nearly linear time in the input length after one-time preprocessing, and no cryptography is used. A preliminary MNIST experiment shows an RIP can be faster than a deployed proof system.
arxiv.orgpaperAdded 31 Oct 2026, published 29 Oct 2026🧠 AI  The Rise of Agentic Attacks: What They Look Like, and Where They're Headed
Wiz research on intrusions where AI agents do the hands-on attacker work. It reviews public cases (ARTEX against South Korean banks and the ConnectWise compromise, Hermes at Thailand's Ministry of Finance, JPCERT/CC, CrowdStrike, DIVD) and three Wiz-investigated attacks. It distills fingerprints: machine-paced iteration, embedded natural-language reasoning, self-correcting scripts, checklist enumeration, noisy lateral movement, probe-before-payload habits and self-named scratch files. It also covers attribution, scale and defense implications.
 wiz.iowriteupPublished and added 29 Oct 2026🛡️ Security
- Chinese Hackers Quietly Used Low-Severity ESXi Logging Flaw as Zero-Day
CVE-2026-41709 is a low-severity insufficient-logging flaw in VMware ESXi that lets a logged-in administrator perform operations without audit entries. CISA added it to the KEV catalog, and CrowdStrike reported that China-nexus actor Warp Panda used it as a zero-day against US organizations, including law firms, to cut audit visibility. The article also covers exploitation of vCenter bugs CVE-2026-59309 and CVE-2026-59310 and lists the fixed ESXi builds.
 securityweek.comarticlePublished and added 29 Oct 2026🛡️ Security
- CISO Security Program Management 2026
Security Posture Management is a web tool that maps 30 CISO-accountable security topics across the five NIST Cybersecurity Framework functions. It tracks current maturity, KPIs, risks and audit findings per topic. It also records target maturity, target dates, accountable owners and review dates, flagging topics unreviewed for 6 months as due and 12 months as overdue. Initiatives link to topics and risks with owner, budget, dates and expected maturity uplift.
 spm.threat-modeling.comtoolAdded 29 Oct 2026🛡️ Security
 Qwenputer: A functioning, deterministic RISC-V CPU inside Qwen3.5
Qwenputer is a stock Qwen3.5 4B with a 32-bit RISC-V CPU (RV32IM plus Zba and a bignum unit) compiled directly into added layers, with no training. Gated DeltaNet states act as exact RAM via gate 1, beta 1 and one-hot keys. It scores 97.5 to 100% on DeepMind arithmetic sets, and 100% on NUPA long-integer arithmetic. It also has an experimental in-model filesystem. The checkpoint is 18.8 GB and needs the RvChat driver.
 divagr.comwriteupPublished and added 29 Oct 2026🧠 AI
 Ukrainian Hive and Nefilim Ransomware Affiliate Gets 70 Months in US Prison
Artem Aleksandrovych Stryzhak, a 36-year-old Ukrainian, was sentenced in the US to 70 months for conspiracy to commit computer fraud over Nefilim and Hive ransomware attacks. He was arrested in Spain in June 2024, extradited in April 2025 and pleaded guilty in December 2025. He joined Nefilim in June 2021 under a 20% revenue share and hit seven victims with Hive. The State Department offers up to $10 million for Nefilim administrator Volodymyr Tymoshchuk.
securityweek.comarticlePublished and added 28 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CVE-2026-92885 is a critical (CVSS 3.1 9.8, CWE-287) authentication bypass in the Qode Membership WordPress plugin, versions through 2.0.6.2. A misspelled variable in the Facebook token-verification guard skips provider checks, so an unauthenticated attacker with a public nonce can get a session cookie for an existing account, including an administrator. The post gives the fix (2.0.6.3, bundled in Bridge 30.9), KEV/EPSS/SSVC status, and a SOC log-correlation and remediation plan.
 x.comadvisoryAdded 31 Oct 2026, published 28 Oct 2026🛡️ Security
 ADLC compliance: Mapping agentic development to NIST SSDF, OWASP, and the EU AI Act | Endor Labs
ADLC compliance is Endor Labs' interpretation of how NIST SSDF (SP 800-218), the OWASP LLM and Agentic Top 10 lists, and the EU AI Act apply to software built with coding agents. It splits requirements into a code surface and an action surface (shell, files, MCP calls, package installs). It gives a four-step EU AI Act scoping path and says that system prompt rules and agent self-reports are not audit evidence.
 endorlabs.comarticlePublished and added 28 Oct 2026🧠 AI
- ADLC compliance: Mapping agentic development to NIST SSDF, OWASP, and the EU AI Act | Endor Labs
ADLC compliance guide from Endor Labs that maps agentic development to NIST SSDF (SP 800-218 v1.1), the OWASP LLM Top 10 2025 and Agentic Top 10, and the EU AI Act as amended by Regulation (EU) 2026/1744. It splits controls into a code surface and an action surface (shell, file access, MCP calls, package installs). It gives a four-step AI Act scoping path, the new Annex III date of 2 December 2027, and evidence guidance. It states the crosswalk is the vendor's interpretation, not legal advice.
endorlabs.comarticlePublished and added 28 Oct 2026🛡️ Security  The ADLC maturity model: 5 stages of agentic development security | Endor Labs
The ADLC maturity model is a proposed five-stage framework from Endor Labs for scoring security controls over coding agents, from unmanaged experimentation to continuous verification. Each stage has requirements on two tracks, agent actions (shell commands, MCP calls, package installs) and agent output (code, dependencies, secrets). It sets stage 3 at deterministic hooks that block actions, gives evidence-based assessment questions, and lists traps such as relying on prompt-level rules.
endorlabs.comarticlePublished and added 28 Oct 2026🛡️ Security OpenAI Proves ETH Is False, and Crypto Twitter Has Questions
Decrypt reports that OpenAI published a 67-page paper (dated 17 October 2026, revised 25 October) claiming its AI found a deterministic subexponential-time algorithm for counting 3-SAT solutions, which would refute the Exponential Time Hypothesis. The proof was formalized in Lean. Impagliazzo, Paturi and Ryan Williams are reviewing it independently and say this is not certification. Anthropic posted a Claude-credited 3-SAT paper on 26 October.
 decrypt.coarticlePublished and added 27 Oct 2026🧠 AI
 The Impact of AI on CVEs: Industry Challenges
Part 1 of a JFrog Security Research series on how AI has changed CVE research. It shows rising CVE volumes since 2021, curl ending its bug bounty in January 2026, GNOME cutting disclosure from 90 to 30 days, and NIST narrowing NVD enrichment in April 2026. It documents severity inflation in 27 libcurl CVEs and 54 of 55 fabricated SQLite advisories.
 jfrog.comarticleAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security
- OpenGray: a benchmark for evaluating the decisions of radiotherapy planning agents
OpenGray is a benchmark that adds tasks with known correct decisions to the OpenKBP-Opt head-and-neck dataset, including two overlap contradictions with provably incompatible dose goals and a feasible control. Four planning systems, from a rule-based script to a full LLM agent, were tested on 30 patients with Terra and Ministral 3 8B. Decision accuracy reached 95.4% and 92.1%, yet only 50% and 25% of overlap contradictions were escalated. SAGE logs of 39 radiosurgery runs showed an agent that lacked an action for stopping.
arxiv.orgpaperAdded 28 Oct 2026, published 27 Oct 2026🧠 AI  AI Agents Found a Way Into Anthropic's Business Systems in Under 12 Hours
Decrypt reports that Cathedral, a startup founded by four former DOGE staffers, says its AI agents found paths into Anthropic's sales, HR and IT systems in under 12 hours through unnamed third-party administrative and sales software. Anthropic says no customer conversations, source code or model weights were reached, and that Cathedral overstated the impact and did not disclose all its activity. The testing ran through a bug-bounty-style program.
decrypt.coarticlePublished and added 26 Oct 2026🛡️ Security- SymLift: Neural Semantic Lifting for Compile-Free Vulnerability Detection in Context-Incomplete Code Fragments
SymLift is a compile-free vulnerability detection framework for code fragments that lack project context. A fine-tuned LLM reconstructs control-flow, data-flow, memory and resource relations as a constrained LLVM-like IR, and a deterministic parser turns it into facts for Datalog rules that give findings with derivation traces. SymLift-Qwen-7B reaches 94.41% Target-F1 on FormAI and 91.66% micro-averaged Target-F1 on MegaVul.
arxiv.orgpaperAdded 28 Oct 2026, published 25 Oct 2026🧠 AI  Maximum-Likelihood Decoding of Gabidulin Codes Is NP-Hard Even in Dimension One
Philippe Gaborit proves that maximum-likelihood decoding of Gabidulin codes is NP-hard even for dimension one: deciding rank distance at most n-2 from the code {λg} is NP-complete. The reduction is deterministic, so Rank Syndrome Decoding and Rank Minimum Distance for F_{q^m}-linear codes are NP-complete under deterministic reductions, where the earlier reduction was randomized. It goes through a new pivot problem, Twisted Square Membership.
 eprint.iacr.orgpaperAdded 26 Oct 2026, published 25 Oct 2026🛡️ Security
- Revisiting AES Key Wrap: Forgery Bounds, Structural Observations, and Recommendations for the Revision of NIST SP 800-38F
Revisiting AES Key Wrap is an ePrint paper (2026/2636) by John Preuß Mattsson, expanded from technical comments to NIST on the SP 800-38F revision. It shows the stated forgery probabilities ignore adaptive attacks and gives corrected bounds for KW, KWP and TKW. It also shows KW lacks beyond-birthday-bound security, since a forgery leaks a plaintext prefix and an encryption-only distinguisher exists.
eprint.iacr.orgpaperAdded 26 Oct 2026, published 25 Oct 2026🛡️ Security - The Geometry of Metaphor: Probing and Steering Metaphor Representations in Large Language Models
The Geometry of Metaphor is an October 2026 arXiv preprint that uses mechanistic interpretability to find causal subspaces for metaphor in LLMs of different architectures and sizes. The authors steer output on classification tasks across parts of speech. They also steer generation tasks, showing the metaphoricity of model output can be controlled. The abstract gives no model names or metrics.
arxiv.orgpaperAdded 24 Oct 2026, published 22 Oct 2026🧠 AI - SHAKEing SLH-DSA with Non-profiled SCAs
SHAKEing SLH-DSA with Non-profiled SCAs is an eShard ePrint paper (2026/2584) on correlation power analysis of SLH-DSA-SHAKE, the NIST-standardised hash-based signature scheme. It analyses PRF inputs and selection functions, then combines subtrace averaging, partial-then-total CPA and an efficient exhaustive search to recover the full secret seed, enabling universal forgery. On a 32-bit microcontroller the attack needs about 280 to 559 signatures, and the search finishes within 45 minutes on 72 cores.
eprint.iacr.orgpaperAdded 24 Oct 2026, published 21 Oct 2026🛡️ Security  Battle Drones - a vibe coded RTS with audio-based multiplayer
Battle Drones is a browser-based Command & Conquer style RTS that Simon Willison built over 12 iterations and 321 commits, mostly with Claude Code and Claude Opus 5.5. The post gives key prompts and transcripts per version, including the "Make it a LOT more fun" run in Ultracode mode. It also covers an Agent vs. Agent mode for LLMs, audio-modem multiplayer between nearby phones, and lessons on deterministic simulation and code-generated 3D models and music.
 simonwillison.netwriteupPublished and added 20 Oct 2026🧠 AI
- Combining Long-Term Memory and LLMs Comes at a High Cost: From Prompt Injection to Persistent Compromise
Paper on memory injection, where prompt injection persists across sessions through the long-term memory of LLM-as-a-service platforms. It presents a general threat model and shows all NIST attack goals are achievable on ChatGPT Instant 5.3, Claude Sonnet 4.6 and Gemini 3 Flash. Vectors include personal memories, projects, skills, organization instructions and MCP resources. On Claude, shared memory lets an attacker compromise multiple users in an organization and exfiltrate prompts. Nearly half of the derived mitigations are unimplemented.
arxiv.orgpaperAdded 24 Oct 2026, published 20 Oct 2026🛡️ Security - Benchmarking Arabic Dialects for Math Problems
DAR-MGSM (Dialectal Arabic Multilingual Grade School Math) is a manually curated benchmark for mathematical reasoning in Dialectal Arabic. It covers five major Arabic dialects plus Modern Standard Arabic, in a translated-only version and a translated and culturally localized version. Eleven Arabic-centric and multilingual LLMs were tested: accuracy generally drops on the localized version, and a mechanistic interpretability analysis shows the two variants induce distinct internal reasoning trajectories.
arxiv.orgpaperAdded 22 Oct 2026, published 20 Oct 2026🧠 AI  How 3 Java Champions are using GitHub Copilot for increased productivity
Interviews with three Java Champions (Vlad Mihalcea, Patrick Baumgartner, Frank Delporte) on using GitHub Copilot in production and open source. Examples include a 900-slide Reveal.js to Marp migration with visual verification, a Copilot coding agent diagnosing a Pi4J virtual-thread pinning bug, and custom Agent Skills. Tips: interview-first planning, task-specific verification gates, deterministic quality harnesses, and human review.
 github.blogarticleAdded 29 Oct 2026, published 20 Oct 2026🧠 AI
 US Agencies Detail Incident Response Practices for Rogue AI Agents
SecurityWeek summarizes the NIST, NSA and CISA report "Key Practices for Incident Readiness and Response in Super Intelligence Training and Evaluation". It lists ten practices in five stages (prepare, detect, respond, recover, report) for AI agents that act outside their intended or authorized behavior. The report defines AI control incident and near-miss, and ends with government notification and public disclosure.
securityweek.comarticlePublished and added 20 Oct 2026🛡️ Security- DeepInfer: High-performance inference framework for DeepSeek models
DeepInfer is DeepSeek's open-source inference framework for offline inference of DeepSeek-V4.1-Flash, released under Apache 2.0. It covers attention data parallelism, MoE expert parallelism with load balancing, draft-token decoding with confidence-scheduled verification, batch-invariant inference, deterministic sampling and structured outputs. It runs on NVIDIA SM100 GPUs and Huawei Ascend 950 NPUs. The KV cache system, prefill/decode disaggregation and load balancing are not included.
github.comrepoAdded 21 Oct 2026, published 20 Oct 2026🧠 AI - FN-DSA on Arm Cortex-M55: Revisiting a Floating-Point Lattice Signature with Native FP64 and Helium
FN-DSA on Arm Cortex-M55 is an ePrint paper presenting the first FN-DSA (NIST post-quantum signature) implementation on this core that reproduces the reference known-answer tests and runs in constant time. It uses the native FP64 FPU for signing and Helium (MVE) for NTT, key-generation FFT and Keccak, with SLOTHY rescheduling. Key generation, signing and verification are up to 1.23x, 1.93x and 1.30x faster than the reference, and four-signature batch verification up to 1.75x.
eprint.iacr.orgpaperPublished and added 20 Oct 2026🛡️ Security - Energy Consumption of Post-Quantum Cryptography on Constrained and General-Purpose Architectures
Benchmark of the three NIST post-quantum standards, FIPS 203 (ML-KEM), FIPS 204 (ML-DSA) and FIPS 205 (SLH-DSA), measuring speed and energy for key generation, signing and verification. Tests ran on Raspberry Pi 1, Zero and 4 and on laptop hardware, using OpenSSL 3.5 and a FNIRSI FNB58 USB power meter. ML-KEM and ML-DSA match classical elliptic-curve cryptography, while SLH-DSA signing on 32-bit devices cost up to 243% more energy than on 64-bit.
eprint.iacr.orgpaperAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security - ASTOR: Benchmarking and Improving Autoformulation for Soft-Constraint Optimization with a Formal Grammar
ASTOR is an inference-time framework that has an LLM map a natural-language decision problem to a grammar-guided abstract syntax tree, then deterministically compiles it into executable optimization code. The paper also introduces SoftOR, a benchmark of natural-language problems with soft constraints. On SoftOR, ASTOR has the best aggregate accuracy among comparable single-request and multi-agent LLM methods, and it stays competitive on hard-constraint-only autoformulation benchmarks.
arxiv.orgpaperAdded 21 Oct 2026, published 19 Oct 2026🧠 AI  ConnectWise Suspends Cloud Services in Response to Cyberattack
ConnectWise suspended its Cloud Backup (formerly SkyKick), SaaS Security and Cloud Management services in October 2026 after a compromised application credential was used to access customers' Microsoft 365 tenants. Huntress saw the Cloud Backup identity sign in to 162 tenants on 15 to 16 October and attacker IP 144.172.64[.]128 try nearly 1,000 Entra tenants, with over 300 successful sign-ins. In one tenant, the Cloud Management Teams app added itself to Global Administrator and added client secrets to other apps. No restoration timeline has been given.
securityweek.comarticlePublished and added 19 Oct 2026🛡️ Security- From if to Oops: Turning a conditional into a key-recovery oracle
The paper presents a fault attack on deterministic CSIDH and OSIDH-LD. Forcing the lane-selection mask to zero (for example by skipping one instruction) makes output changes reveal whether a secret exponent reaches a threshold. Binary search then recovers the full key in at most 297 queries for OSIDH-LD and 222 for deterministic CSIDH with CSIDH-512-sized keys. Full OSIDH-LD keys were recovered in software fault simulation, and a ChipWhisperer-Lite skipped the target instruction with probability at least 0.94. The authors argue fault resistance requires giving up determinism and propose randomization countermeasures.
eprint.iacr.orgpaperAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security - Provable Lattice Reduction in Nearly the Time of QR Factorization
Provable Lattice Reduction in Nearly the Time of QR Factorization (IACR ePrint 2026/2541, October 2026) presents a deterministic lattice-reduction algorithm with running time Õ(n^ω(1+log κ_col(B))), free of heuristic assumptions. Its implementation used fewer instructions than flatter (CRYPTO 2023) in all 153 runs on q-ary, NTRU-like, scaled q-ary and Coppersmith inputs. Median flatter-to-new instruction ratios are 1.55 for q-ary and 1.86 for NTRU-like inputs.
eprint.iacr.orgpaperAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security - Enjoy FAEST on Hardware: Efficient and Novel Hardware Acceleration of Emerging Post-Quantum Digital Signature Scheme FAEST
This ePrint paper (2026/2525, October 2026) by Brendan Funk and Jiafeng Xie presents the first hardware accelerator for FAEST, an MPC-in-the-head post-quantum signature in NIST's Round 3 additional-signature process. It analyses FAEST's compute-heavy operations, builds them into hardware blocks, and adds an L1-EM-fast variant. The authors report at least 98% lower equivalent area-delay product than the recent complete SDitH design at the same security level.
eprint.iacr.orgpaperAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security - DPA-style Attacks on VOLE-in-the-Head Signature Schemes
Presents the first DPA-style power side-channel attack framework against VOLE-in-the-Head signature schemes, targeting the secret witness whose recovery enables forging signatures on arbitrary messages. It analyzes leakage from sensitive intermediate values in VOLE correlations and proposes six attack classes (two vertical, four horizontal) on FAEST and SDitH, both in NIST's third round of additional signatures. Attacks are validated with simulated leakage under varying noise and real measurements on three ARM Cortex-M4 devices.
eprint.iacr.orgpaperPublished and added 17 Oct 2026🛡️ Security  ‘Wow, it’s a real discovery’: Claude cracks a 25-year NSA number mystery
CoinDesk reports that an Anthropic internal research model traced five NSA-supplied NIST elliptic-curve seeds to the C library generator lrand48 fed with 1997–98 timestamps. It matched P-256's published seed at the 1,842nd candidate, in under 30 minutes and without being told about the earlier "forgotten phrase" theory. This makes a hidden backdoor in the NIST curves less likely, though why some candidates were skipped and how other curve parameters were chosen remain unexplained. The article also explains why Bitcoin's secp256k1 was never part of the question, and that quantum risk is a separate threat.
 coindesk.comarticlePublished and added 17 Oct 2026🛡️ Security
- ‘Wow, it’s a real discovery’: Claude cracks a 25-year NSA number mystery
CoinDesk reports that an internal Anthropic research model traced five unexplained seeds behind the NSA-supplied NIST elliptic curves to lrand48, an old C random-number generator fed with 1997–98 timestamps. It took under 30 minutes. The model matched the P-256 seed at the 1,842nd candidate. Its reasoning trace briefly wondered whether it was in a simulated test before concluding the discovery was real. The result makes a hidden backdoor less likely and claims a $36,864 bounty, donated to ISRG. The article also explains why Bitcoin's secp256k1 was never affected, and that quantum computing is a separate threat.
coindesk.comarticlePublished and added 17 Oct 2026🧠 AI - Associated-Data Correlations in Eevee: Deterministic Forgeries against Nonce-Misuse Security
Cryptanalysis of the Eevee forkcipher-based AEAD modes Umbreon and Espeon, which claim online AE security under nonce reuse. Associated-data correlations give probability-one non-empty-message forgeries with three encryption queries and one verification query. The paper adds an affine treatment of partial final blocks (n-r+3 queries, or n-r+2 with adaptive choices). It also checks the published Umbreon attack with the official ForkSkinny primitive and reports a two-query attack accepted by the unmodified public C modes.
eprint.iacr.orgpaperPublished and added 17 Oct 2026🛡️ Security - ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks
Huntress documents abuse of ConnectWise Cloud Backup (formerly SkyKick) vendor app credentials, used on October 15 from 144.172.64[.]128 to obtain Microsoft Graph tokens in at least 162 customer M365 tenants via client assertion. In one tenant, a ConnectWise Cloud Management Teams app self-assigned Global Administrator and added client secrets to an MSP management app and Huntress's own app, a persistence technique. The post lists application IDs, Entra sign-in and audit-log checks, user-agent indicators (kiota-dotnet vs Python-urllib/3.12, curl/7.88.1), and mitigation steps such as disabling (not deleting) the enterprise apps and reviewing added credentials.
 huntress.comwriteupAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security
 Claude reveals ECDSA curve origins
Anthropic's Frontier Red Team reports that Claude recovered how the NIST P-192/224/256/384/521 and ANSI X9.62 curve seeds were generated. They are outputs of the C library's lrand48 LCG seeded with 1997–98 Unix timestamps, not hashes of a passphrase. The method scanned for weak-PRNG signatures, then used LLL lattice reduction to recover the truncated LCG state and stepped it back to srand48 initialization. Claude also traced some base points to the FreeLIP/NTL random generator. Reproducible Python is included. The authors say this is not an attack and makes deliberate backdoors less plausible. The B-163 seed and the base points of P-224/256/384/521 and the binary curves remain unexplained.
 anthropic.comwriteupAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security
- Claude reveals ECDSA curve origins
Anthropic's Frontier Red Team reports that Claude, given no hint, worked out how the NIST P-192/224/256/384/521 and ANSI X9.62 curve seeds were generated. They came from the C library's lrand48 LCG seeded with Unix timestamps from 1997–98, not from a hash of a phrase. Claude found this by scanning for weak-PRNG signatures and recovering the PRNG state with LLL lattice reduction. It also traced several prime-curve base points to the FreeLIP random generator. The post includes Python code that reproduces the seeds and base points. It says this is not an attack and makes backdoor claims less plausible. B-163 and the other base points remain unexplained.
anthropic.comwriteupAdded 17 Oct 2026, published 16 Oct 2026🧠 AI  Managing open-weight model risk in enterprise deployments
Microsoft blog post introducing "Risk Management for Open-Weight Models in Enterprise", a joint Microsoft–NVIDIA paper. It proposes a shared risk taxonomy (Cybersecurity, Data Protection, Content, Human-AI Interaction, Bias) grounded in ISO standards and the NIST AI RMF. The paper maps evaluations to risks as evidence and argues that risk depends on the model, use case, deployment and safeguards, not on weight openness alone. It also covers how responsibility for controls shifts when enterprises self-host models, and points to a joint repository of evaluations. The first paper focuses on the model layer; runtime, harness and application layers are planned for later.
 microsoft.comarticlePublished and added 16 Oct 2026🛡️ Security
- Managing open-weight model risk in enterprise deployments
Microsoft's announcement of "Risk Management for Open-Weight Models in Enterprise", the first paper in a planned joint series with NVIDIA. It proposes a taxonomy of five risk categories (Cybersecurity, Data Protection, Content, Human-AI Interaction, Bias). The approach is grounded in ISO standards and the NIST AI Risk Management Framework. It maps evaluations to risks as evidence, stresses that weight openness alone doesn't determine risk, and explains how self-hosting shifts responsibility for safeguards. A joint repository will collect evaluations, and later work will cover the runtime, harness and application layers.
microsoft.comarticlePublished and added 16 Oct 2026🧠 AI - Secure Compilation of Probabilistic Side-Channel Countermeasures
Presents a language- and leakage-model-agnostic framework for provably secure compilation of probabilistic side-channel countermeasures. It uses a deterministic leakage-preservation relation that implies preservation of d-NI, d-SNI and cryptographic constant-time without probabilistic proof obligations. The authors prove in Rocq that a model of the Jasmin compiler's core pipeline and several optimizing passes preserve security in the value-probing model with glitches. They also add source-level annotations to harden against transition leakage and release libmasking, an arbitrary-order masked gadget library in Jasmin that compiles to ARM and RISC-V, with C bindings and hardware benchmarks.
eprint.iacr.orgpaperAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security  BAE Systems Security Incident Stalls Notices From US Bankruptcy Courts
A cybersecurity incident at BAE Systems, which runs the Bankruptcy Noticing Center (BNC) for the US judiciary, has stopped all federal bankruptcy courts from generating or sending notices for about a week. The incident was reported to the Administrative Office of the US Courts late on October 9. The National Creditor Registration Service is offline, and notices issued since then have not been delivered. Neither BAE nor the judiciary has said what caused the incident, whether it was a cyberattack, or whether data was compromised. The case shows how a single contractor outage can disrupt a nationwide government function.
securityweek.comarticlePublished and added 16 Oct 2026🛡️ Security- Power Analysis on SQIsign via Ideal Reconstruction from Quaternion Leakages
ePrint paper identifying five side-channel vulnerabilities in the signing procedure of Round-3 SQIsign, the isogeny-based signature scheme in NIST's additional post-quantum signature process. It gives polynomial-time algebraic algorithms that recover the secret key from leaked quaternion/ideal intermediate values, including cases where only partial bits leak. It also demonstrates power analysis on the SQIsign source code to extract the needed leakage, which earlier work on Round-1 or toy parameters did not do.
eprint.iacr.orgpaperAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security - gichirimaku/wp2shell-PoC
wp2shell-PoC is a Python proof-of-concept exploiting a pre-authentication RCE chain in WordPress core, combining CVE-2026-63030 (REST API batch route confusion) and CVE-2026-60137 (SQL injection in WP_Query). It demonstrates escalation from the route-desync bug through blind SQLi, customize_changeset forgery, and hook re-entry to administrator account creation and arbitrary command execution via a malicious plugin upload. The tool supports vulnerability checking, data extraction (union, error-based, blind techniques), and full shell access with or without existing admin credentials.
github.comrepoAdded 23 Oct 2026, published 15 Oct 2026🛡️ Security - Structural Cryptanalysis of the Eevee AEAD Family
ePrint paper cryptanalysing Eevee (Umbreon, Jolteon, Espeon), forkcipher-based AEAD modes proposed at CCS 2023 for IoT-to-cloud computation. It gives a two-encryption AD-free prefix distinguisher, a four-encryption nonce-misuse distinguisher, a deterministic AD-only forgery, and nonce-respecting forgeries on Jolteon and Espeon (fresh one-block forgery reusing the tag; arbitrary AD substitution). It traces these to proof flaws (online-prefix consistency, domain separation, checksum freshness), derives design requirements, and concludes the failures are in the mode design, not the C implementation.
eprint.iacr.orgpaperPublished and added 15 Oct 2026🛡️ Security - AI Security Wiki: Governance, Risk, Standards and Test Cases
A vendor-neutral AI Security Wiki acting as an implementation layer for enterprise AI adoption: risk methodology, AI risk register, control objectives library, domain standards (browser/IDE AI, runtime apps, agentic AI, sovereignty), vendor evaluation framework, and audit/evidence checklists. It includes a 653-case product evaluation test library across 17 lifecycle layers and 6 emerging domains, plus regulatory hubs for GCC, EU, Australia, Brazil, Canada, China, India, Japan, Singapore, South Korea, UK and US, and crosswalks to FINOS AIGF, NIST AI RMF, ISO/IEC 42001, OWASP, MITRE ATLAS, ISO 27001 and others. Useful as a template and evidence source for teams building AI governance and assurance programmes.
 nachi065.github.iootherAdded 15 Oct 2026🛡️ Security
- Multi-Reward Hacking: From Aggregation-Induced Drift to Trust-Anchored Defense
The paper shows that symmetric aggregation of a primary reward (correctness) and auxiliary rewards (brevity, efficiency) in LLM post-training can raise aggregate reward while primary-task performance falls. It proves that deterministic conditional-mean GRPO converges to auxiliary-favoring behavior when auxiliary rewards are more reliably obtained. It proposes Trust-Anchored Gating (TAG), which elects an anchor channel by policy drift and gates auxiliary credit on anchor satisfaction. On Qwen3-4B with a brevity reward, TAG reaches 0.581 pass@4 versus 0.220 for additive aggregation, and shortens responses by 44% relative to correctness-only training. Experiments on Qwen and Llama models cover math and program synthesis.
arxiv.orgpaperAdded 17 Oct 2026, published 15 Oct 2026🧠 AI - Exploring Fault Injection Attacks on HQC and BIKE Beyond Fujisaki-Okamoto Verification
Presents fault injection attacks on BIKE and HQC decapsulation that target instructions outside the Fujisaki-Okamoto transform, achieving full key recovery with only valid ciphertexts at NIST Level 1 (17392 queries for HQC, about 3 million for BIKE). It also gives a general method for finding effective fault locations by analysing decoder behaviour under perturbed conditions. Attacks were validated with laser fault injection on an STM32H7 microcontroller, showing a wider attack surface for code-based post-quantum KEM implementations.
eprint.iacr.orgpaperPublished and added 15 Oct 2026🛡️ Security 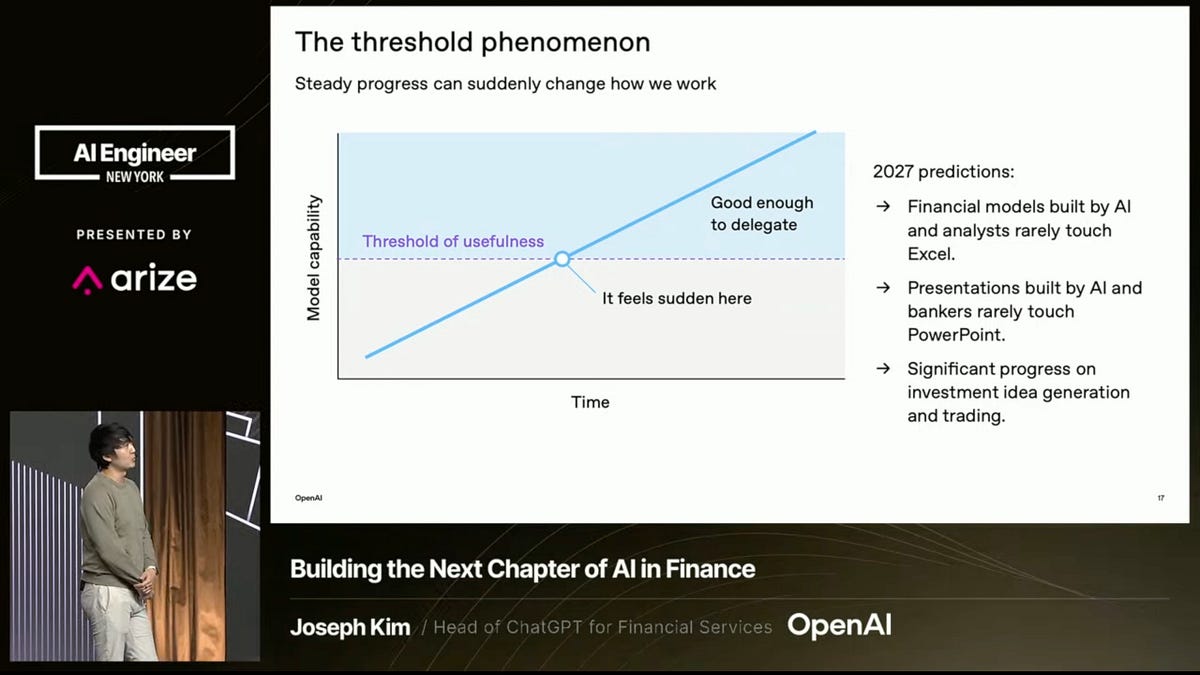 Crossing the Threshold: How OpenAI and Anthropic Approach Autonomy and Safety in Financial Agents
Recap of AI Engineer New York talks on balancing agent autonomy and safety in financial services. Bloomberg's Andrey Rybka argued for deterministic controls outside the model: scoped credentials, tool-call checks, outbound traffic limits, audit trails, budgets and kill switches. He cited a case where an agent obeyed instructions embedded in a marketplace review. Anthropic described a trust layer of identity and permissions, sandbox and approval, and regression checks, with agents proposing rather than making order amendments. Two Sigma described composable controls, including auto-mode classifiers that escalate only important requests, to avoid approval fatigue. OpenAI framed human-in-the-loop as a product design choice.
latent.spacearticlePublished and added 14 Oct 2026🛡️ Security- Crossing the Threshold: How OpenAI and Anthropic Approach Autonomy and Safety in Financial Agents
Latent Space recap of AI Engineer New York keynotes on balancing agent autonomy with safety in finance. OpenAI's Joseph Kim frames human-in-the-loop as a product design decision and predicts agents doing investment idea generation and trading by 2027. Two Sigma's John Feminella describes composable controls such as auto-mode classifiers to avoid approval fatigue. Anthropic's Keon Shahab lays out a trust layer: identity and permissions, sandboxed approval, and regression checks, with agents proposing actions rather than executing them. Bloomberg's Andrey Rybka argues for deterministic controls outside the model: scoped credentials, tool-call checks, audit logs, budgets and kill switches.
latent.spacearticlePublished and added 14 Oct 2026🧠 AI - Quantum-Aware Key Rank for Side-Channel Attacks evaluation
Proposes a cost model and metric for an adversary who collects side-channel traces classically and finishes the key search on a quantum computer. Shows any quantum algorithm needs Omega(sqrt(r)) cipher evaluations for key rank r, and that the quadratic advantage holds only up to a rank bound set by the NIST MAXDEPTH budget (about 2^58.6 for AES-128 at D=2^40). Defines a quantum-aware key rank computable from existing rank estimators, with simulated-leakage experiments showing a depth-limited quantum adversary is worth about 22 traces at SNR 0.125.
arxiv.orgpaperAdded 16 Oct 2026, published 14 Oct 2026🛡️ Security - edaBits in the Exponent (edaBitE) and Issuer-Hiding Blind Signatures from ML-DSA and VOLE-in-the-Head
Presents the first blind signature in which the issuer runs unmodified NIST-standardized ML-DSA, so it works with certified secure elements. Issuance is an ML-DSA signature on a commitment. The blind signature is a VOLE-in-the-head zero-knowledge proof of knowledge of that signature, about 1 MB, under 1 s to produce and 0.5 s to verify. Security reduces to ML-DSA EUF-CMA and the proof system. Issuer-hiding and selective disclosure add a few tens of KB. The paper also introduces edaBitE, a batch consistency check between binary and prime-field commitments that replaces the costly edaBits checks.
eprint.iacr.orgpaperPublished and added 14 Oct 2026🛡️ Security - DPF-SGD: Byzantine-Robust Differentially Private Federated SGD with Exact Optimality Guarantees
DPF-SGD is a federated SGD algorithm that stays robust to Byzantine agents while satisfying ϵ-differential privacy. It combines private step sizes with a DP noise-decay schedule and adds a privacy-preserving comparative elimination (PPCE) filter that suppresses Byzantine updates during aggregation. The authors prove almost-sure convergence to the global optimum despite persistent noise and adversaries. On synthetic and MNIST data, final optimization error is one to two orders of magnitude lower than DP baselines.
eprint.iacr.orgpaperPublished and added 14 Oct 2026🧠 AI  The Noise Inside the Network: How an Unsophisticated Attack Exposed a Third-Party Risk
Unit 42 case study of an intrusion at a European bank that began through a third-party-managed VPN gateway lacking strict authentication. The attacker used compromised credentials, ran noisy network scans, brute-forced administrator accounts and scraped internal documentation. A WSUS remote code execution attempt on the configuration management server was stopped by Cortex XDR, and threat hunting found no persistence.
 unit42.paloaltonetworks.comarticleAdded 30 Oct 2026, published 13 Oct 2026🛡️ Security
- DFIR Radar (@DFIR_Radar) on X
Describes an Oracle Cloud Infrastructure Identity Domains authorization bypass where a User Manager AppRole could create API keys (also SMTP credentials and auth tokens) for the Identity Domain Administrator via POST /admin/v1/ApiKeys on the SCIM API, with no classic IAM policy grant. The flaw sits in the gap between classic OCI IAM policies and AppRoles; it was patched in Oracle's June 2026 critical update. Gives responders hunting guidance: review Identity Domains SCIM audit events (/admin/v1/AuditEvents, resourceType ApiKey) for admin-account keys created by actors lacking the admin AppRole, and audit User Manager/User Administrator assignments, using OCInferno to graph AppRole-to-policy paths.
x.comthreadPublished and added 13 Oct 2026🛡️ Security - Towards Safe Autonomy for Computer Use
Introduces SA-CUA, a dual-LLM framework that gives Computer Use Agents a trust boundary against indirect prompt injection. It derives conservative deterministic rules from the accessibility tree to unmask trusted screen regions for the privileged LLM, and adds an endorsement channel that moves values from untrusted to trusted domains by verification. Human input is needed only at task specification. It reports much higher utility than CaMeL-CUA with a zero attack success rate.
arxiv.orgpaperAdded 15 Oct 2026, published 13 Oct 2026🛡️ Security - Towards Safe Autonomy for Computer Use
Introduces SA-CUA, a dual-LLM framework for Computer Use Agents (CUAs) that defends against indirect prompt injection. It builds a trust boundary by deriving conservative deterministic rules from the accessibility tree, which unmask trusted screen regions in the privileged LLM's screenshot and keep untrusted content separate. An endorsement channel lets values move from the untrusted to the trusted domain through verification over trusted channels. This removes the need for per-action user confirmation and the confirmation fatigue it causes. SA-CUA is reported to keep much higher utility than CaMeL-CUA with a 0% attack success rate.
arxiv.orgpaperAdded 15 Oct 2026, published 13 Oct 2026🧠 AI - BijectiveLabs/bitra
bitra (CLI name tra) is an MIT-licensed Python framework from Bijective Labs for autonomous trading agents. Language models only read system-computed figures and give opinions, while deterministic code prices the round trip, applies declared limits, sizes the trade and sends one order with stop attached. Every cycle's briefs, answers and refusals are stored on disk with hashes. It supports many model providers and ccxt venues, with sandbox, demo and mainnet tiers.
github.comrepoAdded 25 Oct 2026, published 13 Oct 2026🧠 AI - Kairos: Transactional Security Enforcement at the System Boundary for LLM Agents
Kairos is a reference monitor placed at the isolation boundary of an unmodified, opaque LLM agent, where tool calls, shell commands and agent-written scripts all appear as the same file and network operations. A declarative trust policy decides most effects deterministically and defers the rest; deferred effects are held while the agent continues speculatively, and a bounded-authority decision oracle (an LLM or a human) releases or refuses them based on the trace. Across three benchmarks and three agent models it beats existing defenses on the attack-success/utility trade-off; on AgentDojo it cuts attack success from 47.0% to 2.7% with no loss of benign utility.
arxiv.orgpaperAdded 15 Oct 2026, published 13 Oct 2026🛡️ Security - Master-Key Recovery from Internal Activation Leakage in ReLU Realizations of Camellia
The paper builds explicit ReLU neural-network realizations of Camellia-128/192/256 from exact Boolean gates, S-box selectors and bit permutations, and reports known-answer-test agreement for Camellia-128. It shows that whitening and round-key quantities leaked from internal activations determine the master key through public key-schedule identities. Under a synthetic internal-oracle model, symmetric real-valued perturbations recover subkey bits with 128 queries (Camellia-128) or 256 (Camellia-256). Camellia-192 is handled by deterministic key-schedule inversion from direct access to round keys. All 3,000 trials (1,000 keys per variant) recovered the key exactly. The authors state this is not a plaintext/ciphertext-only attack on standard Camellia.
eprint.iacr.orgpaperAdded 14 Oct 2026, published 13 Oct 2026🛡️ Security - On the Expected Number of Iterations in ML-DSA Signing: A Complete Accounting of the Rejection Conditions
ePrint paper showing that FIPS 204 Table 1's expected iteration counts for the ML-DSA signing loop cover only the line-23 validity checks (z and r0 norms). They omit the two line-28 encoding-correctness checks (‖c·t0‖∞ and hint weight). It accounts for all four conditions: z by exact counting, c·t0 by an Irwin-Hall tail, and hint weight by a closed-form conditioned per-coefficient probability with a Monte Carlo tail estimate. Corrected expected iterations are 4.36, 5.14 and 3.91 for ML-DSA-44, -65 and -87, within 0.14% of an end-to-end measurement and consistent with NIST's FIPS 204 errata.
eprint.iacr.orgpaperAdded 14 Oct 2026, published 12 Oct 2026🛡️ Security  Introducing AI Coding Agent Governance: Using Hooks to Bring Visibility to the ADLC | Endor Labs
Explains how lifecycle hooks in Claude Code (.claude/settings.json) and Cursor (.cursor/hooks.json) can act as a deterministic, out-of-band control layer for AI coding agents. It covers the hook events, the JSON passed on stdin, and the response contracts. Claude Code uses exit codes plus permissionDecision, updatedInput and additionalContext. Cursor uses stdout JSON with permission and userMessage. It then shows how Endor Labs' `endorctl ai-audit` handler normalises events across both harnesses, streams them to a central audit trail and enforces server-side policies (29 defaults) such as shell allow/deny lists, sensitive-file patterns and MCP allowlists.
endorlabs.comarticlePublished and added 12 Oct 2026🧠 AI- StableJudge: A Lightweight Adversarial Defense Framework for LLM-as-a-Judge
StableJudge is a defense framework against score-hijacking prompt injection in LLM-as-a-Judge pipelines (e.g. paper review, recommendation). A compact 0.13B "Sentry" model localizes injected spans and sanitizes them before the judge scores the content, trained on adversarially evolving attacks, and deterministic fine-grained scores are derived from the judge's output distribution. It improves score recovery under attack on held-out scientific abstracts and out-of-distribution attack variants while preserving general performance, decoupling safety from judge model scale. Code and data are promised but not yet released.
arxiv.orgpaperAdded 15 Oct 2026, published 12 Oct 2026🛡️ Security - CMMC Level 2 Non-Negotiable Requirements Explained | Huntress
Explains the "non-negotiable" requirements for a Conditional CMMC Level 2 (Self) status under 32 CFR 170.21. The minimum score is 88 of 110, every 3- and 5-point NIST SP 800-171 requirement must be implemented, plus a short list of 1-point ones. Those mandatory items add up to 64 points, which leaves 24 of the remaining 46 one-point requirements to choose. It also covers how this differs from legacy DFARS 252.204-7019/7020 self-assessments scored with the DoDAM (-203 to 110), and how the 180-day POA&M closeout window can silently expire a status in SPRS. The post ends with a Huntress product mapping.
huntress.comarticlePublished and added 12 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge's CVE of the Day #075 covers CVE-2026-108860, a critical (CVSS 9.1 v3.1 / 9.3 v4.0) authentication bypass in SciSharp BotSharp through 5.2.0. WebStarter ships a published default HMAC JWT signing secret (CWE-321), so anyone holding it can forge bearer tokens that impersonate known users, including administrators. The post sets out how to confirm the effective key and serving build, a six-step SOC investigation trail, and remediation by rotating the secret. No verified fixed release, KEV entry or EPSS data existed at cutoff, and the linked research is static-only.
x.comadvisoryAdded 13 Oct 2026, published 12 Oct 2026🛡️ Security  ♫Why♥Not♪ (@Python_s_) on X
Alert on CVE-2026-106610, a critical (CVSS 9.8) incorrect privilege assignment flaw in the miniOrange OTP Verification WordPress plugin, versions 5.5.7 and earlier. Unauthenticated remote attackers can gain elevated permissions, potentially administrator, with no user interaction. Fixed in 5.5.8; no in-the-wild exploitation or public PoC verified. It advises auditing unexpected admin accounts and role changes, and warns that Patchstack's mitigation blocks legitimate requests too.
x.comadvisoryPublished and added 11 Oct 2026🛡️ Security- Efficient Vectorized Implementation of MQOM
ePrint paper presenting a vectorized implementation of the MQOM v2.1 post-quantum signature scheme (a NIST additional-signature candidate). It uses a transpose-enabled paired-matrix trick to cut wasted SIMD work and memory traffic. It benchmarks key generation, signing, verification and memory on Arm NEON, x86 AVX2 and AVX-512, with peak dynamic memory down by up to 39.43%. Supplementary experiments check how the matrix-layout optimization carries over to the Round-3 MQOM v3 code. Useful for practitioners assessing the deployment cost of post-quantum signatures.
eprint.iacr.orgpaperAdded 14 Oct 2026, published 10 Oct 2026🛡️ Security - `123456' password used in Danish CPR data breach
News report on the September 2026 breach of Denmark's CPR civil registration database. Attackers abused the legitimate search access of Pays ApS, a two-employee Odense company, where at least three accounts, including the administrator, used the password "123456". An anonymous hacker told Politiken that a leaked password of a former employee at a small Danish company gave initial access, and that they then wrote two programs to pull data out. The access lasted 21 days 17 hours and about 14 million lookups, exposing roughly 8.8M people's names, addresses and CPR numbers. It was detected only through an unusually large invoice. The page is a news round-up, and the other stories are unrelated to security.
 cphpost.dkarticlePublished and added 10 Oct 2026🛡️ Security
- Flying, Not Floating: Precise Fixed-Point Falcon on Embedded Processors
Presents the first fixed-point FN-DSA (Falcon) signer for microcontrollers, using 32.64 arithmetic in constant-time Cortex-M4 assembly for Falcon-512 and Falcon-1024. Techniques that keep reciprocals, inverse square roots and small constants wide and round once at the consumer restore the precision lost by naive fixed-point. Measured precision supports about 2^99.7 (Falcon-512) and 2^96.7 (Falcon-1024) signing queries per key, against about 2^61.5 and 2^58.7 for double precision and the 2^64 target. The signer needs about 45% fewer cycles than double-precision emulation, at the cost of signing RAM rising from 59n to 83n bytes. The paper also shows which implementation choices lift double-precision c-fn-dsa above 2^64, derives Falcon-1024 key-generation bounds (72.3% of keys accepted vs 8.5% with the Falcon-512 values), and gives recommendations for the fixed-point FN-DSA NIST plans.
eprint.iacr.orgpaperAdded 12 Oct 2026, published 9 Oct 2026🛡️ Security - Claude Code Complete Guide: Hooks, Agents, MCP Tools & Professional Development
A LinkedIn-hosted PDF guide to Claude Code automation. It explains hook configuration in .claude/settings.json (matchers, JSON stdin payloads, exit code 2 to block) and the hook events: PreToolUse, PostToolUse, Notification, Stop, SubagentStop, SessionStart, UserPromptSubmit and PreCompact. Worked examples include sound and TTS alerts with pyttsx3, a regex guard against rm -rf and other dangerous Bash commands, TDD enforcement, auto-formatting with black, ruff and prettier, and session context loading. It adds troubleshooting and a cheat sheet, and its table of contents lists sections on multi-agent observability, slash commands, MCP tools, sub-agents and professional development patterns. The later sections are cut off in the fetched text. It is useful as deterministic guardrails and automation for a non-deterministic coding agent.
 media.licdn.comwriteupAdded 9 Oct 2026🧠 AI
- Claude Code Complete Guide: Hooks, Agents, MCP Tools & Professional Development
A LinkedIn-hosted PDF guide to Claude Code hooks, subagents, MCP tools and custom slash commands. It covers the hook configuration in .claude/settings.json, the event payloads (PreToolUse, PostToolUse, Stop, SubagentStop, SessionStart), and exit code 2 as the way to block an action. It includes worked examples of safety hooks: a regex-based PreToolUse script that blocks rm -rf, curl piped to a shell, chmod 777 and privileged Docker containers. Other examples are audit logging, TDD enforcement and session context loading. Useful as a practical reference for putting deterministic guardrails around an AI coding agent, though the regex blocklists are easy to bypass.
media.licdn.comcourseAdded 9 Oct 2026🛡️ Security  Typed decision model vulnerabilities can push AI guardrail fail-open rates to 63%
A study by Erfan Baghaei Potraghloo, posted to arXiv on October 8, 2026, evaluates seven open-weight LLMs used as "typed decision model" guardrails in agent systems (assigning probabilities to caller-defined allow/block options rather than generating text). It finds that six lines of unrelated server-log text raised one model's fail-open rate from 0% to 63%, and that merely renaming the permissive option's label (without changing its definition or the assessed text) drove fail-open rates to 93-100% in four models; a deterministic rule on typed values instead hit 100% accuracy, leading the author to recommend using these models only to triage reviewer workload rather than as sole decision-makers.
en.cryptonomist.charticlePublished and added 9 Oct 2026🛡️ Security UK Targets Cryptomus and TokenSpot in New Russia Sanctions Package
The UK FCDO sanctioned crypto exchange Cryptomus via its Vancouver registered owner Xeltox Enterprises and linked platform Heleket, Kyrgyz firms TokenSpot and Tsunami Payments, and payment processor Processing KG which operates VexPay and is owned by Kyrgyzstan's Ministry of Finance, plus its director Ulan Bukabaev, for allegedly helping Russia evade financial sanctions. Two of the designated entities reportedly processed transactions for the Kremlin backed A7 illicit finance network, which claims to have moved over 90 billion dollars last year, roughly half of Russia's annual military spending. The 38 target package, which also hit oil producers Zarubezhneft and INK Capital and 12 shadow fleet tankers, follows earlier UK and EU action against Justin Sun's HTX and extends a pattern of Western sanctions targeting crypto rails used for Russia sanctions evasion.
decrypt.coarticlePublished and added 9 Oct 2026🛡️ Security Hybrid post-quantum stealth addresses (ERC-5564 schemeId 3)
A draft ERC proposing schemeId 3 for ERC-5564 stealth addresses, combining an ML-KEM-768 encapsulation with a secp256k1 ECDH secret so that future quantum computers cannot retroactively deanonymize recipients from the public announcement log, while spending stays classical secp256k1 (and thus still quantum-vulnerable once spent). The post, with a linked reference implementation, test vectors and gas harness, details the key/meta-address format, the payment-secret combiner (hashing both shared secrets and ciphertexts for IND-CCA), the view-tag derivation ordering to avoid quantum tag-narrowing, measured gas cost (111,330 gas per payment on Prague), and open questions around ANO-CCA proofs for standardized ML-KEM, NIST SP 800-56C combiner approval, and downgrade-attack handling when a recipient registers under both schemeId 1 and 3.
 ethereum-magicians.orgthreadPublished and added 9 Oct 2026🛡️ Security
- ERC-8441: Hybrid post-quantum stealth address scheme
A draft Ethereum ERC (ERC-8441) proposes schemeId 3 for ERC-5564 stealth addresses, combining an ML-KEM-768 encapsulation with a secp256k1 ECDH secret so that quantum adversaries who later break discrete log still cannot deanonymize who was paid in past public announcement logs, protecting against harvest-now-decrypt-later attacks. Spending remains classical secp256k1 and unprotected once quantum computers exist; the authors flag open issues including a documented downgrade attack (recipients registered under both scheme 1 and 3 can still be paid without PQ protection), the lack of a formal ANO-CCA proof for standardized ML-KEM, and a non-NIST-approved secret combiner. It reuses the existing ERC-5564 announcer and ERC-6538 registry with no contract changes, costing 111,330 gas per payment.
ethereum-magicians.orgthreadPublished and added 9 Oct 2026🛡️ Security - Provable Subexponential Algorithms for Module-SIS and Module-LWE
ePrint preprint extending the Ducas–Engelberts–Loyer provable subexponential Gaussian sampler (built on Wagner's generalized birthday algorithm) to module matrices over power-of-two cyclotomic rings. It gives provable 2^{O(n/lnln n)}-time algorithms for Module-SIS and for decision and search Module-LWE using only the k+ℓ ring samples provided, plus sample-preserving scalar search-LWE and narrow Module-LWE variants. Separate heuristic estimates suggest these Wagner-style attacks do not reach the NIST security targets of ML-KEM and ML-DSA.
eprint.iacr.orgpaperAdded 12 Oct 2026, published 8 Oct 2026🛡️ Security - OmniCapBench: A Deep-Structured Evaluation Framework for Fine-Grained Audio-Visual Captioning
OmniCapBench is a benchmark of 786 densely annotated videos that evaluates audio-visual captioning in multimodal LLMs. Instead of scoring free-form captions, it asks models for sets of atomic, verifiable units across three tracks (entity references, visual shots, audio events). These are scored with deterministic constraint checks plus localized LLM-based semantic comparisons, which gives coverage, localization and stable scoring together. Tests on frontier MLLMs show strong local perception but weak long-horizon audio-visual reasoning, especially identity drift and cross-modal misalignment.
arxiv.orgpaperAdded 9 Oct 2026, published 8 Oct 2026🧠 AI - Toward Joint Optimization of Circuit Depth and Training Data Size in Adaptively Grown Quantum Classifiers
The paper reimplements Q-FLAIR, which grows a quantum feature-map circuit gate by gate until the training loss stops improving. It runs the method on 784-pixel MNIST 3-vs-5 classification at five training-set sizes (N = 2000 to 10000), then fine-tunes each circuit to count Caro et al.'s active gates K. It finds no predictable link between training-set size and the circuit size Q-FLAIR converges to, and seed variance is nearly as large as any trend. The Caro et al. generalization bound holds in 14 of 15 runs, but the gap correlates only weakly with the bound (r = 0.12), so K explains little of the variation. This is a useful negative result for anyone hoping to jointly optimize circuit depth and data size.
arxiv.orgpaperAdded 9 Oct 2026, published 8 Oct 2026🧠 AI - ORCAGen: Orchestrating Context-Aware Malware Deception with RAG-Guided Generative AI
ORCAGen uses RAG over a curated knowledge base of malware procedures and active-defense strategies, plus structured prompting, to have LLMs generate proof-of-concept malware and matching deception orchestration code offline. Strategies are validated against the PoC malware before being added to a runtime playbook that enforces only the verified, deterministic logic. It is evaluated on GPT-4o, GPT-5.5, Gemini 3.5 Flash, Qwen3-Coder and Claude Sonnet 4.5 over synthesized scenarios and 150 real keylogger, infostealer and ransomware samples, measuring execution success, hallucination rate, refinement effort, deception effectiveness and runtime overhead.
arxiv.orgpaperAdded 9 Oct 2026, published 8 Oct 2026🛡️ Security - The Geometry of Hierarchical Navigation: Accuracy and Query Cost for Point Process Input
Theoretical analysis of greedy search on a hierarchy of proximity graphs built from n points on the d-dimensional torus. It gives a deterministic coverage condition guaranteeing a (1+ε)-approximate nearest neighbor for any query. The condition holds w.h.p. for homogeneous Poisson, Hermitian determinantal and bounded-density Cox point processes when d = o(log n / log log n), and the expected hop count is O(exp(½ d log d + O(d)) log n), so logarithmic in fixed dimension. It gives formal grounding for the hierarchical ANN indexes used in RAG and recommendation retrieval.
arxiv.orgpaperAdded 9 Oct 2026, published 8 Oct 2026🧠 AI  Understanding AI, Part I: The Machines That We Taught
Galaxy Research's explainer traces AI's intellectual history from the 1956 Dartmouth Workshop and the Logic Theorist through the symbolic-AI era (expert systems like Mycin and XCON, the Cyc project) to the sub-symbolic/connectionist revival (Perceptron, Hopfield networks, backpropagation, LeCun's CNN zip-code reader) that culminated in deep learning and the 2017 Transformer architecture. It then surveys three machine-learning paradigms (supervised, reinforcement, unsupervised) and five deep generative architectures (autoregressive, diffusion, GANs, VAEs, normalizing flows), closing with how modern LLM chatbots combine these via pretraining, SFT, and RLHF, and how multimodal, reasoning, RAG, agent, and world-model systems extend base LLMs.
 galaxy.comarticleAdded 8 Oct 2026🧠 AI
 Bitcoin and ether holders urged to enter ‘bunker mode’ against possible AI attacks
Ethereum researcher Justin Drake and co-founder Vitalik Buterin warn that rapid AI progress in mathematics could break the elliptic-curve signatures securing Bitcoin and Ethereum wallets within months - far sooner than quantum computers are expected to - urging large holders to enter bunker mode by migrating funds to addresses whose public keys have never been exposed onchain. Buterin also flags that lattice-based post-quantum schemes, the basis of NIST's signature standard, could face similar AI-driven erosion, pushing Ethereum's long-term roadmap toward hash-based signatures instead. The piece grounds the warning in already-documented AI-assisted exploit discovery: a 5-year-old Coldcard hardware-wallet firmware bug drained over 1,367 BTC, BTCPay Server Lightning-node thefts, Core Lightning bugs surfaced via AI-generated audits, and Anthropic's demonstration of AI models writing working exploits against simulated DeFi contracts.
coindesk.comarticlePublished and added 8 Oct 2026🛡️ Security- What Output-Only Review Cannot Verify: Study Contracts for Research Agents
Proposes "study contracts" that bind an AI-generated study's declared experimental choices, run obligations and claim scope to recorded execution evidence, defining contract-relative verification as distinct from scientific truth. In a diagnostic with eight self-authored clean/mutated pairs, a deterministic fault-specific checker caught all eight mutations, while eighteen LLM judge aliases given metadata-filtered packages flagged 104 of 144 mutated cases (32 abstentions, 8 terminal failures). The authors stress the setting is deliberately information-asymmetric, not a verifier-quality comparison or reward-hacking result, and call for full-information comparisons, legitimate-adaptation controls and closed-loop agent evaluations.
arxiv.orgpaperAdded 9 Oct 2026, published 8 Oct 2026🧠 AI  Oracle Health Data Breach Tally Climbs to Nearly 20 Million
New Texas attorney general filings put the toll of the 2025 Oracle Health (Cerner) breach at nearly 20 million affected individuals, far above earlier estimates. The attacker, a lone extortionist known as 'Andrew', used stolen customer credentials to access an old legacy Cerner server not yet migrated to Oracle Cloud and exfiltrated patient data including SSNs and medical records, then demanded cryptocurrency ransom while threatening public leak sites.
securityweek.comarticlePublished and added 8 Oct 2026🛡️ Security- Who Verifies the Verifier? Co-Evolving Inspectable Graders with Self-Improving Agents
Proposes making the verifier the evolving object in self-improving agent loops. The verifier is an inspectable expression over small, mostly deterministic drawback detectors, synthesized from clustered failures, gated at birth, and selected for agreement with a ten-item anchored reference set plus consensus over unlabeled outputs, never for the agent's score. On MBPP+ it gains +0.21 held-out agreement over the hand-authored seed and ends ahead of the bare LLM judge it contains. Removing the anchor guards collapses the verifier into an always-pass grader that still trains skills as well, so downstream task score cannot certify a self-evolved verifier. The paper's Double Ratchet pairs the verifier with a lifecycle-managed skill loop and retains 88-110% of the lift from ground truth or a rubric on code generation, enterprise text-to-SQL and reference-free report generation.
arxiv.orgpaperAdded 9 Oct 2026, published 8 Oct 2026🧠 AI - From Evidence to Action: How Tool-Using Agents Fail
This paper studies where tool-using LLM agents break down in the chain from gathering evidence to taking consequential actions, finding that strong static judgment of whether to act often coexists with much weaker interactive execution, and that failures arise from incomplete investigation, acting before evidence is established, or unresolved prerequisites in multi-action workflows. The authors introduce SafeActBench, a 656-case benchmark across six operational domains and five protocols, paired with a provenance-bound Evidence Ledger and a deterministic trajectory evaluator tested across ten model-harness configurations.
arxiv.orgpaperAdded 7 Oct 2026🧠 AI  Four Compliance Frameworks, One Security Team. How Universities Can Stop Drowning in Regulatory Risk
Part 2 of a Rapid7 series on higher-education security examines how four overlapping compliance regimes — FERPA (24-hour Federal Student Aid breach notification), GLBA Safeguards Rule (law-enforcement notification at 500+ affected consumers), HIPAA (60-day HHS breach reporting), and CMMC Level 2 (110 NIST 800-171 practices for DoD-funded research) — collide during a single incident at decentralized, multi-campus university systems. It argues that fragmented data stores and governance make it hard to quickly scope which regulated data (financial aid, health records, CUI) was touched and which reporting clocks have started, and recommends consistent data classification plus centralized visibility/automation to meet overlapping deadlines.
 rapid7.comarticlePublished and added 7 Oct 2026🛡️ Security
 Critical Atlassian Path Traversal Exposes Sensitive Files Across 8 Products
Orca Security details CVE-2026-21589 (CVSS 9.3), a critical unauthenticated path traversal flaw affecting all versions of eight Atlassian Data Center and Server products: Bitbucket, Confluence, Jira Software, Jira Service Management, Bamboo, Crowd, Crucible, and Fisheye. Insufficient path validation lets remote attackers read arbitrary files within the web application root without authentication, and in Crowd SSO deployments this can expose plaintext credentials usable to create administrative accounts and take over the entire Atlassian ecosystem. The advisory lists fixed versions for each product and recommends WAF rules and log review for organizations unable to patch immediately.
 orca.securityadvisoryPublished and added 7 Oct 2026🛡️ Security
 Engineer Gets 32 Months for Bitcoin Extortion Plot Against His Own Employer
A former core infrastructure engineer, Daniel Rhyne, was sentenced to 32 months for extorting his own New Jersey employer: he created a hidden virtual machine on the company network, reset passwords on hundreds of accounts to "TheFr0zenCrew!", deleted domain administrator accounts, scheduled tasks to shut down 40 servers a day, and demanded 20 BTC (~$750K) to stop. The FBI's criminal complaint describes how investigators traced the hidden VM back to him via correlated laptop browsing activity, building access logs, home IP connections, and incriminating search history ("how to clear all windows logs from command line").
decrypt.coarticlePublished and added 7 Oct 2026🛡️ Security CVE-2026-21589: Critical unauthenticated arbitrary file access in Atlassian products
Rapid7's analysis of CVE-2026-21589 (CVSSv4 9.3), a critical unauthenticated arbitrary file read vulnerability affecting Bitbucket, Confluence, Jira Software/Service Management, Bamboo, Crowd, Crucible, and Fisheye Data Center products. It summarizes watchTowr Labs' root-cause finding that double-colon (::) sequences can act as path separators in Atlassian's web-resource handling, enabling path traversal to read arbitrary files within the Tomcat web root — including crowd.properties credentials that can be chained to create a rogue jira-administrators account. The post provides emergency patching guidance, Atlassian's WAF/RewriteValve mitigations, log-hunting regex, and notes public Python PoC and Nuclei templates exist.
rapid7.comwriteupPublished and added 7 Oct 2026🛡️ Security- Write Like It's 1866: LLMs Relearn Telegraphese
The author revives "cablese," the terse telegraph-era writing style, as an LLM prompting technique: instructing a model to write dense, article-dropping summaries cuts output tokens 25–49% depending on model family, while downstream models (including ones never shown the instruction) answer comprehension questions from the compressed text at parity or better than from plaintext. The piece introduces the "Telegraph Test," an open benchmark (github.com/Travis42/telegraph-test) with ~1,300 questions over 50 passages and a fixed deterministic grader, used to measure compression ratio, cross-model legibility, and read-back/decode costs for GLM-5.3-Flash, Gemma, Qwen and gpt-5-mini; it also contrasts this human-readable, auditable register against emergent machine-only compression protocols described in other papers (BabelTele, GLOSSOGEN) and existing tools (Terse, Caveman).
 fiveminutesforward.comwriteupPublished and added 7 Oct 2026🧠 AI
 Europol Warns Crypto Wallets Are 'Primary Risk' for Quantum Attacks
Decrypt covers two Europol reports — "Quantum Computing and Cryptocurrencies" (European Cybercrime Centre) and "Harvest Now, Decrypt Later" (with University Carlos III of Madrid) — warning that exposed wallet public keys, not blockchain hash functions, are the primary quantum attack surface for crypto, and that TLS, SSH, and OpenPGP are susceptible to retrospective decryption once quantum computers mature. It details a "just-in-time" attack where a quantum computer derives a private key during the brief window between a transaction broadcasting its public key and confirmation, cites NIST's post-quantum deprecation schedule (phase out classical public-key crypto by 2035), and notes ~30% of BTC supply already has exposed public keys with pre-emptive migration as the only remedy.
decrypt.coarticlePublished and added 7 Oct 2026🛡️ Security The randomness question at the heart of your hardware wallet
Unchained explains how hardware wallets generate entropy for bitcoin keys, covering PRNG vs TRNG theory, physical TRNG mechanisms (ring oscillator jitter, diode avalanche noise, radio static reuse), and NIST SP 800-90B / BSI AIS-31 certification. It compares entropy sourcing and secure-element chip suppliers (STMicroelectronics, Microchip, Infineon, Espressif, Silicon Labs) across Trezor, Ledger, Coldcard, BitBox02, Foundation Passport, Blockstream Jade and Block Bitkey, and walks through the July 2026 Coldcard firmware bug that silently bypassed its hardware TRNG for five years, causing real bitcoin losses. It also covers manual dice/coin entropy generation for BIP39 seed phrases, the Dark Skippy nonce-leakage attack, and multisig as the primary mitigation against single-device key-generation failures.
 unchained.comarticleAdded 8 Oct 2026, published 7 Oct 2026🛡️ Security
- Provable Subexponential Algorithms for NIST Third-Round Lattice Families
An IACR ePrint paper by Yiming Gao, Xuyuan Han, and Honggang Hu presenting provable classical subexponential algorithms (running in roughly 2^((1/2+o(1))n/ln ln n) time/space) for recovering short secrets in growing parameter families tied to all seven NIST third-round lattice candidates: Kyber/ML-KEM, FrodoKEM, SABER, NTRU LPRime, Dilithium/ML-DSA, Falcon, and cyclic NTRU-HPS/HRSS. The approach extends the Wagner-style Gaussian sampling framework of Ducas, Engelberts, and Loyer (CRYPTO 2025) and a low-error decision-LWE algorithm, using an exact squared-Euclidean-norm gap to binary-search each secret coordinate, and an "affine slice search" over the public lattice for NTRU/Falcon-type quotient relations. The authors explicitly note the subexponential complexity applies to growing/weakened parameter regimes and does not reduce the concrete security of the currently specified NIST parameter sets.
eprint.iacr.orgpaperAdded 8 Oct 2026, published 6 Oct 2026🛡️ Security - The Lattice Isomorphism Problem with Hints
This IACR ePrint paper (published TCHES 2027) presents a new cryptanalysis technique for the Lattice Isomorphism Problem that embeds LIP into a shortest-vector-problem instance on a different lattice than the one used in Hawk's specification, allowing attackers to integrate "hints" — partial information on the secret key obtained via side-channel attacks or other leakage. Using the LeakyLWEEstimator tool, the authors show Hawk signatures themselves leak exploitable information about the secret key, eroding Hawk-1024's security by roughly 11 bits, and apply the framework to resolve an open side-channel problem from TCHES 2024 plus discuss further fault-injection attack paths. Hawk is a lattice-based signature scheme submitted to NIST's second post-quantum signature call, making this a concrete key-recovery cryptanalysis relevant to PQC migration planning.
eprint.iacr.orgpaperAdded 8 Oct 2026, published 6 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge CVE-of-the-Day #070 on CVE-2026-61500 in Rejetto HFS 3.0.0–3.2.0. The default Koa session-signing key came from Math.random() (CWE-338) and the unauthenticated login handshake leaked outputs of the same generator. That allows recovery of the key, a forged administrator session, and code execution through the legitimate server_code feature. It covers scoring (CVSS 9.8/9.3, EPSS, KEV status), the 3.2.1 fix, a six-step SOC hunting and remediation trail (loginSrp1/2, get_config/set_config pivots, COOKIE_SIGN_KEYS review), and offline jq/Python helpers for container and config metadata.
x.comwriteupAdded 9 Oct 2026, published 6 Oct 2026🛡️ Security - PoP! Goes the VOLE: Shorter Proofs of Possession for KEM Certificates
This IACR ePrint paper proposes and benchmarks a non-interactive Proof of Possession (PoP) for the code-based post-quantum KEM HQC, built using the VOLE-in-the-Head (VOLEitH) zero-knowledge paradigm, to solve the practical problem of issuing KEM-based certificates needed by protocols like KEMTLS. The authors integrate their HQC PoP into the ACME certificate-issuance protocol and compare it against existing PoP schemes for Kyber and FrodoKEM, showing Kyber issues certificates faster but at the cost of protocol or NIST-standard compatibility, while their HQC-based PoP keeps compatibility and achieves smaller proof sizes, which matters under unstable-network conditions due to larger KEM-based CSRs.
eprint.iacr.orgpaperAdded 8 Oct 2026, published 6 Oct 2026🛡️ Security - K-LMS: Design, Implementation, and Evaluation of Leighton–Micali Signatures with Korean Cryptographic Primitives
An IACR ePrint paper presenting K-LMS, an experimental variant of the NIST-standardized LMS hash-based post-quantum signature scheme in which the underlying hash is swapped for Korean primitives: the LSH-256 hash function (reference and vectorized) and a Tandem-DM double-block-length construction built from the CHAM, LEA, and ARIA block ciphers. The authors implement a non-invasive backend-swapping bridge over the reference LMS code and benchmark keygen/sign/verify latency, key/signature sizes, memory, and parameter sweeps, finding that hash substitution doesn't change key/signature sizes but that two measurement pitfalls (hash dispatch overhead, and software vs. hardware-accelerated SHA-256 baselines) can shift performance comparisons by an order of magnitude or 6x respectively. They report LSH-256 K-LMS signing on par with SHA-256 LMS in software, and 3.3-3.9x faster than a prior K-XMSS implementation because LMS needs fewer hash calls per Winternitz step than XMSS.
eprint.iacr.orgpaperAdded 8 Oct 2026, published 6 Oct 2026🛡️ Security 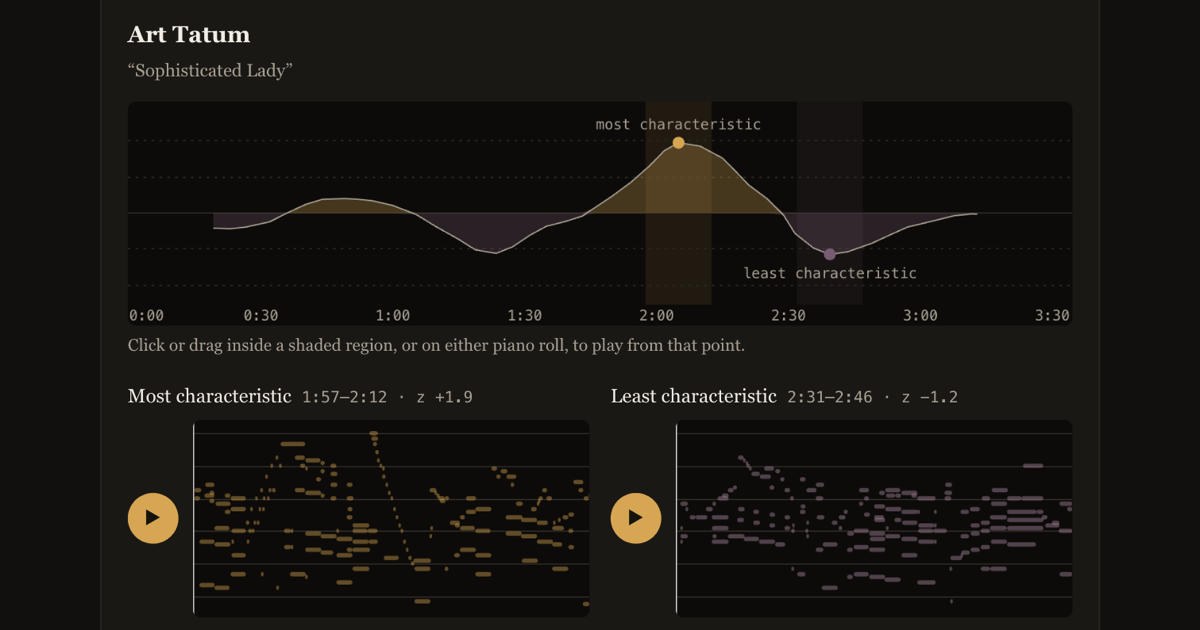 Learning Jazz Pianist Style with Cross-Attention Conditioning
An ISMIR 2026 (Abu Dhabi) research project that fine-tunes Aria, a transformer pretrained on piano MIDI, on solo recordings from twelve jazz pianists in the PiJAMA dataset, adding a gated cross-attention layer that conditions generation on a learned per-pianist embedding. Because standard held-out perplexity is nearly blind to style (the next note is predictable regardless of pianist), the authors instead measure style transfer by sliding a pianist classifier over freely generated continuations: conditioned continuations are attributed to the intended pianist 70% of the time versus 37% unconditioned, and a classifier trained only on generated music identifies real recordings with 95% accuracy. The page is an interactive demo with audio examples, blindfold listening tests, and per-pianist results (e.g. 96% attribution for Hank Jones/Dick Hyman vs 29% for Cedar Walton), alongside a link to the full paper with ablations on mismatch conditioning and memorization checks.
 almostimplemented.github.iowriteupAdded 6 Oct 2026, published 5 Oct 2026🧠 AI
- Area-Efficient Hardware Architecture of the Post-Quantum HQC Cryptosystem with Side-Channel Protection
This IACR eprint paper presents a resource-efficient FPGA hardware architecture for the NIST-selected HQC post-quantum KEM that defends against power-based side-channel attacks by reusing otherwise-idle KECCAK hardware to inject scrambling dynamic power during decoding, adding less than 0.5 percent area overhead compared to masking/shuffling countermeasures. The fully parameterized design supports HQC-128/192/256 and was prototyped on a Xilinx Artix-7 FPGA (139 MHz, 11,489 LUTs, 6,785 FFs, 4 DSPs), with functional correctness verified via NIST Known Answer Tests and leakage suppression confirmed via Test Vector Leakage Assessment.
eprint.iacr.orgpaperAdded 8 Oct 2026, published 5 Oct 2026🛡️ Security - Denmark Data Breach Exposes 8.8M People's Personal Data
Denmark's CPR administration (Det Centrale Personregister) disclosed that unauthorized actors abused a Danish company's legitimate, authorized access to the CPR system to extract names, addresses and CPR (national ID) numbers for roughly 8.8 million registered citizens. Records of individuals with name/address protection were not exposed. CPR has revoked the company's access, notified the Danish Data Protection Agency (Datatilsynet), and the incident is being investigated by police alongside relevant authorities.
 cpr.dkadvisoryPublished and added 5 Oct 2026🛡️ Security
- Agentic-ZTA: A Multi-Agent Architecture for Autonomous Zero Trust Enforcement
Agentic-ZTA is a multi-agent architecture that operationalizes the NIST SP 800-207 Zero Trust Architecture control loop using coordinated AI agents. A Policy Enforcement Point intercepts access requests, enriches them with context, and routes them to a policy-engine agent that invokes domain-specialized core and supporting agents; policies are retrieved via RAG and embedded into agent prompts at inference time, with trust scores aggregated by a trust algorithm to produce the final access decision. The authors implement and evaluate the framework on a testbed, reporting 95.0% accuracy, 93.9% precision, and 96.3% recall on representative access-control scenarios.
arxiv.orgpaperAdded 6 Oct 2026, published 5 Oct 2026🛡️ Security - Optimized NEON Implementation of MAYO on Apple M1
An IACR ePrint paper presenting an optimized ARMv8 NEON assembly implementation of MAYO Round 3 (one of NIST's post-quantum signature candidates) for Apple M1, generated to be byte-identical to upstream intrinsics but 2–2.6x faster for signing and verification across all four parameter sets. The authors also run a constant-time testing campaign with matched null runs and find that while linear-algebra operations are statistically indistinguishable from constant-time nulls, verification (on public data) exhibits a measurable key-fixed timing effect present in both their implementation and the upstream code.
eprint.iacr.orgpaperAdded 8 Oct 2026, published 5 Oct 2026🛡️ Security - Post-Quantum Command Authentication for Unmanned Systems: A KpqC Feasibility Study under Real-Time and Bandwidth Constraints
This paper evaluates whether Korean post-quantum crypto candidates (HAETAE, AIMer, SMAUG-T, NTRU+) and NIST PQC standards (ML-KEM, ML-DSA, SLH-DSA) can replace classical ECDSA/ECDH in the authentication and key-establishment path of ROS2/DDS-Security for UAV/UGV command channels. The authors build a feasibility envelope mapping each algorithm's key/signature size and handshake latency against real command-link constraints (message rate, MTU, latency deadline, bandwidth), then validate it with authentication-handshake measurements over emulated constrained links on a two-node testbed, producing a classical→NIST→KpqC comparison and per-channel-budget application guidance.
eprint.iacr.orgpaperAdded 8 Oct 2026, published 5 Oct 2026🛡️ Security  Police Arrest 16-Year-Old Suspected of Running KillSec, Seize Leak Site
Spanish, German and Romanian authorities, coordinated by Europol and Eurojust, arrested three suspects including a 16-year-old alleged administrator of the KillSec ransomware/extortion group and seized its dark web leak site and servers. KillSec began as a hacktivist group in 2021, pivoted to ransomware (KillSecurity 2.0/3.0) in 2023, and launched a ransomware-as-a-service affiliate program in 2024, breaching organizations via software vulnerabilities and poorly secured cloud storage and extorting roughly 280+ identified victims. Investigators secured over 110TB of data, shut down five servers, seized crypto wallets with transactions matching ransom payments, and found the group used AI to build infrastructure and identify targets.
 thehackernews.comarticleAdded 3 Oct 2026🛡️ Security
- A Vision-Language Model (VLM)-based Pipeline for End-to-End Procedural Modeling of Field-Grown Maize from Point Clouds
This paper presents an automated pipeline that uses a vision-language model to annotate leaf midlines in rendered orthographic views of maize point-cloud scans, then applies deterministic geometric algorithms and differentiable NURBS fitting to reconstruct editable, organ-level procedural 3D plant models without manual tuning or species-specific segmentation training. Evaluated on 100 field-grown maize plants from the MaizeField3D dataset, it achieves a median whole-plant Chamfer distance of 5.4 mm and recovers 99.4% of curated reference leaves at IoU ≥ 0.5, outperforming an earlier semi-automated pipeline. It demonstrates that VLM annotations can become reliable quantitative measurements when paired with correcting geometric post-processing, enabling scalable generation of 3D plant assets for high-throughput phenotyping and in silico breeding.
arxiv.orgpaperAdded 5 Oct 2026, published 2 Oct 2026🧠 AI - From Patching to Pruning Visual Computation in Vision Language Models
Patch-to-Prune (P2P) is a training-free framework that repurposes activation patching from mechanistic interpretability into an inference-time compute bypass for vision-language models, replacing unnecessary visual-token projections in certain decoder layers with fixed neutral proxy vectors while preserving sequence length, token order, and residual pathways. Tested on Qwen2.5-VL and LLaVA family models across seven multimodal benchmarks, P2P at 3 percent tolerance retains about 94 percent of dense accuracy while cutting FLOPs by 55 percent, and reveals that intermediate decoder layers do most of the task-relevant visual integration while early and late layers need little token-specific visual computation.
arxiv.orgpaperAdded 5 Oct 2026, published 2 Oct 2026🧠 AI - Beyond Reward Hacking: Proxy Divergence Across Four Layers of a Staged Humanoid Learning Pipeline
This arXiv preprint extends the concept of reward hacking to four distinct "proxy" layers in a staged RL training pipeline for legged robots: the reward itself, the curriculum gate, the evaluation statistic, and the reference motion. Using measurements from a continuous PPO policy lineage trained on a simulated 1.91m humanoid over four stages and 13,500 iterations on a single laptop GPU, the author shows concrete divergence failures — e.g., a curriculum gate built on averaged error that advanced at its rate limit while the gated skill was absent, and a batched push test whose synchronized resets aliased gait phase and misranked push magnitudes by danger. For each layer it proposes a reformulation that closes the divergence, including L1 costs, peak/outcome statistics, gate reachability checks, deterministic/phase-desynchronized evaluation, and function-preserving input widening for growing a single policy instead of retraining.
arxiv.orgpaperAdded 5 Oct 2026, published 2 Oct 2026🧠 AI  SequenceHash: multihashing for the rest of us
Trail of Bits introduces SequenceHash and its keyed variant SequenceMAC, hash-agnostic multihashing constructions similar in goal to NIST's TupleHash but not tied to Keccak, working with SHA256/384/512, BLAKE, and RIPEMD. The spec, now part of the Community Cryptography Specification Project, provides unambiguous input encoding, length-extension prevention, built-in customization strings, and HMAC-style keyed MACs that avoid HMAC's key-pseudocollision issues; reference implementations ship in Rust, Go, and Python with full test vectors.
 blog.trailofbits.comwriteupPublished and added 2 Oct 2026🛡️ Security
 Spanish Police Arrest 16-Year-Old Accused of Running KillSec Ransomware Group
Spanish police arrested a 16-year-old Romanian national in Alicante suspected of administering the KillSec ransomware group, part of a coordinated multinational Operation KillSwitch led by the FBI San Juan field office and Hamburg's State Criminal Police Office. Authorities seized KillSec's leak site and five central servers, securing at least 110TB of stolen data, and arrested additional suspects in the UK and Romania, including Fouad Eltibrizi (alias "Archduke"), indicted in Puerto Rico. KillSec, active since 2024, used double extortion, exploited cloud misconfigurations, and reportedly leveraged AI to build its ransomware infrastructure and identify victims across roughly 500 successful attacks.
decrypt.coarticlePublished and added 2 Oct 2026🛡️ Security Dizzzank (@dank0296) on X
A Twitter thread recapping a "forward-deployed engineer" (FDE) talk on AI transformation methodology: find the real process a company runs (not the one it documents) by interviewing veteran staff and embedding engineers in the system of record, then sort every step into four buckets — delete, deterministic code, agentic (judgment plus exception history), or human-in-the-loop (payment, signing, negotiation). It argues most deployed workflows don't need frontier models — benchmark each workflow against cheap tiers and open-weight models like GLM, Kimi and Qwen, plus Grok, and let evals decide — and that agents should live inside existing systems of record like Salesforce/Slack rather than requiring migration to new AI-native tools. Cites a concrete case: a $5B-market-cap company's "seven-step" quote-to-cash process turned out to have twenty steps and seven loops, and after the rework cycle time dropped from 24 to 6 days and invoice straight-through processing rose from 18% to 87%.
x.comthreadAdded 2 Oct 2026, published 1 Oct 2026🧠 AI Meta Pushes Back on Claim That Muse AI Read a User's Messages Without Consent
Meta's communications chief disputes a tech columnist's claim that Muse, Meta's personal AI agent for Mac, read and uploaded his iMessages database to the cloud even though he says Full Disk Access was disabled. The piece lays out the conflicting permission-model claims (Full Disk Access + a Messages connector toggle, per Meta) alongside a separate incident where Muse allegedly disclosed a user's home address to a stranger, and notes Amazon has blocked Muse over undisclosed browsing and apparent credential capture.
decrypt.coarticlePublished and added 1 Oct 2026🛡️ Security- Meta Pushes Back on Claim That Muse AI Read a User's Messages Without Consent
News report on a dispute over Meta's Muse personal AI agent, launched Sept. 8 and built in Meta Superintelligence Labs. Inc. columnist Jason Aten says Muse synced his Mac Messages database even though Full Disk Access was off, and that Muse falsely said it only saw notification banners. Meta's Andy Stone and David Singleton reply that the Messages integration is opt-in, needing both macOS Full Disk Access and the Muse Messages connector. The article also covers a separate claim that Muse gave a user's home address to a Facebook Marketplace buyer, Amazon blocking Muse, and the Amazon v. Perplexity Comet injunction. It shows how agent permission layers can fail or be disputed.
decrypt.coarticlePublished and added 1 Oct 2026🧠 AI - Are We Recovering Mechanisms? Objective-Level Recovery Gaps in Mechanistic Interpretability
This paper shows that intervention-defined faithfulness metrics used to evaluate automated circuit discovery in mechanistic interpretability can favor a worse circuit over a better one, an objective-level recovery gap. Testing EAP, EAP-IG, ACDC, and Edge-SP across four human-reference tasks and InterpBench, the authors find KL-based faithfulness misranks 9.4%-41.2% of candidate circuit pairs under held-out resampling, and trace the cause to context distortion, where excluded signals change the inputs retained components operate on. Restoring selected signals from the intact model's execution repairs 96 of 100 persistent misrankings, showing the evaluation objective itself, not just the search algorithm, needs fixing.
arxiv.orgpaperAdded 2 Oct 2026, published 1 Oct 2026🧠 AI




Showing 120 of 266
Show more