- Show HN: Farol – A risk map of a pull request for the person who approves it
farol is a free, MIT-licensed CLI and GitHub Action that runs after an AI code review and gives the human approver a risk verdict (fast track, quick review, careful review) and a 0-100 score for a pull request. It uses the TypeScript type checker, go/types and Python ast to trace which pages, APIs and jobs a change reaches, and it adds diff coverage, security findings and contract breaks. It never executes or sends code.
 github.comrepoAdded 26 Oct 2026, published 25 Oct 2026🧠 AI
- SnailSploit/Claude-Red
claude-red is an MIT-licensed library of offensive security skills for the Claude Skills system, planned at about 130 skills across 23+ categories (web, Active Directory, cloud, exploit development, EDR evasion and others). Each skill is a SKILL.md file that loads on conversational triggers, so unused skills cost no context. It installs by git clone, sparse checkout per category, install.sh or pasting into a system prompt.
github.comrepoAdded 22 Oct 2026🧠 AI - SnailSploit/Claude-Red
claude-red is a library of offensive security skills for the Claude Skills system, each a SKILL.md file that loads on conversational triggers (for example, mentioning SQL injection loads offensive-sqli). Categories include web, Active Directory, cloud, mobile, exploit development, fuzzing, privilege escalation, post-exploitation and AI. It targets about 130 skills across 23+ categories, with an install script and sparse-checkout install per category. Built on Sahar Shlichov's offensive checklists, MIT licensed.
github.comrepoAdded 22 Oct 2026🛡️ Security - OpenAI CLI
OpenAI CLI is OpenAI's official Go command-line client for the REST API. It lets users generate images, upload and download files, create and wait on batches, call the Responses API, and query admin usage endpoints from a terminal or shell script. It supports JSON, JSONL and YAML output, GJSON transforms, shell completion, and install via Homebrew, go install or release binaries.
github.comrepoAdded 23 Oct 2026, published 22 Oct 2026🧠 AI - Cyber Detective💙💛 (@cyb_detective) on X
Python Cybersecurity Libraries is a curated GitHub list by Yogsec, shared in a post by cyb_detective. It groups Python libraries by task: network analysis, penetration testing, threat intelligence, reverse engineering and malware analysis, forensics and investigation, web application security, CTF, and machine learning for security. The tweet shows only the category names, not the individual libraries.
 x.comrepoAdded 24 Oct 2026, published 21 Oct 2026🛡️ Security
- vxcontrol/pentagi
PentAGI is an open-source, self-hosted multi-agent system that uses LLM agents to carry out penetration testing tasks autonomously. The MIT-licensed repo has a Go backend, a React frontend and GraphQL. It ships Docker Compose files for Langfuse tracing, Graphiti knowledge-graph memory and an observability stack. Topics list OpenAI and Anthropic as model backends.
github.comrepoAdded 20 Oct 2026🧠 AI - better-isms/grcskills
grcskills is a library of 60 plain SKILL.md files in the Agent Skills format, each describing how an experienced practitioner does one piece of governance, risk and compliance work. Examples are scope statements, risk registers, audit prep, vendor review and incident handling. Every skill names where the agent must stop and hand the decision to a person. Installs are pinned to reviewed release tags and checked by a validator.
github.comrepoAdded 20 Oct 2026🧠 AI - better-isms/grcskills
grcskills is an MIT-licensed library of 60 SKILL.md files (Agent Skills format) that let coding agents draft and prepare governance, risk and compliance work: scope statements, statements of applicability, risk registers, audit prep, vendor review, policies, privacy, incidents and continuity. Each skill names where the agent must stop so a person decides. Installs are pinned to release tag v2026.10.19.2, and a validator rejects network commands and credential paths.
github.comrepoAdded 20 Oct 2026🛡️ Security - Saylor (@Kev96790724) on X
G-Krusch is an MIT-licensed, local-first Google Workspace hub built on Node.js 22 and SQLite WAL. It runs a 12-tool MCP server (SSE and Stdio) plus a REST bridge on port 5446 for Drive, Calendar and Gmail. It includes a 1,024-dimension hybrid Drive RAG with an embedding cascade (Ollama bge-large, then Gemini, then offline fallback) and FTS5 BM25. PDF extraction returns page citations. Tokens are kept in an AES-256-GCM vault; 30 of 30 tests pass.
x.comrepoAdded 21 Oct 2026, published 19 Oct 2026🧠 AI - OWASP/MCP-Security-Testing-Guide
OWASP MCP Security Testing Guide is a living, GPL-3.0 collection treating the Model Context Protocol as a security boundary from user through model, MCP client, MCP server and tool to the target system. It covers threats, secure development, host/client controls, supply chain, enterprise gateways, detection, incident response, taxonomy, public incidents, case studies and review checklists, with 79 tests in Chapter 3 (sections 3.1–3.19). It includes a finding template, and it links the MCP Goat lab for safe practice. It is useful to AppSec, red team and SOC people assessing MCP deployments.
github.comrepoAdded 17 Oct 2026🛡️ Security - Show HN: Graphicle, a Rust port of Graphify with memory for coding agents
Graphicle is a local-first Rust program that parses a repository into a tree-sitter code graph (a port of Graphify) and adds project memory: docs, reviewed decisions and captured Claude Code/Codex sessions. It serves cited file-and-line excerpts within a token budget via one MCP server, CLI and browser app, backed by a single SQLite file, with no API key or telemetry. The README reports a code-only extract on Kubernetes (31k files) in 3m18s versus 26m38s for Graphify 0.9.88, and a memory comparison against seven systems. Agent-proposed memories need user approval and go stale when the code they reference changes.
github.comrepoPublished and added 14 Oct 2026🧠 AI  google/embeddinggemma-2
Model card for EmbeddingGemma 2, an open (Apache 2.0) 740M-parameter multimodal embedding model from Google DeepMind built on Gemma 4. It maps text, code, images, video and audio into one 768-d space, with a 270M text backbone and optionally loadable 170M vision and 300M audio encoders, an 8K context, and Matryoshka truncation to 128/256/512/768 dims. The card gives practical guidance: task instruction prefixes, re-normalising after truncation, avoiding float16 (NaN or degraded embeddings), interleaved multimodal inputs with placeholder tokens, and vision token budgets. It targets on-device search, RAG, classification and clustering.
 huggingface.corepoAdded 12 Oct 2026🧠 AI
- bilawalsidhu/gods-eye-view
God's Eye View is an open-source, vanilla JavaScript + CesiumJS + Vite 3D globe that fuses live public feeds (aircraft, ships, satellites, quakes, public cameras, weather) into one explorable scene. Its AI layer is a hands-free voice agent on the OpenAI Realtime API with 30 tools: camera fly-to, whiteboard annotations, analyst queries over live layers, and scene-context and screenshot grounding. Keys stay server-side and the browser gets only a short-lived session token. An experimental ChatGPT/Codex OAuth path is also supported. The app doubles as an MCP server, so Claude Desktop, Codex or ChatGPT can open the globe from a conversation.
github.comrepoAdded 11 Oct 2026🧠 AI - bilawalsidhu/gods-eye-view
God's Eye View is an open-source, vanilla-JavaScript CesiumJS and Vite client that puts live aircraft, ships, satellites (SGP4), earthquakes, fires, public CCTV and mapped ALPR cameras on one photorealistic 3D globe. It adds cockpit tracking, FLIR/NVG sensor shaders and a voice agent built on the OpenAI Realtime API. It works without API keys, and the docs cover server-side key brokering with SSRF protection, localhost binding and a SECURITY.md threat model. For OSINT/GEOINT practitioners it is a hackable base for fusing public signals, with an explicit rule against person-tracking features.
github.comrepoAdded 11 Oct 2026🛡️ Security - argoproj-labs/mcp-for-argocd
TypeScript MCP server for Argo CD that lets MCP clients (Cursor, VS Code, Claude Desktop) list, inspect, create, update, delete and sync applications, read logs and events, and run resource actions through natural language. It supports stdio and HTTP stream transports, with a stateless mode for multi-replica Kubernetes deployments. The security design is detailed: API tokens are read only from env vars or headers and never from tool arguments, the default token is bound to the default base URL, a per-host token registry covers extra instances, a read-only mode disables write tools, and the HTTP listener binds loopback by default and requires an inbound auth token if exposed.
github.comrepoAdded 10 Oct 2026🧠 AI - Show HN: Edi Life OS – self-hosted life dashboard with an MCP server for AI
Edi Life OS is a self-hosted dashboard (PHP 8.1+, MySQL, vanilla JavaScript) that combines focus timer, habits, goals, Kanban tasks, finances and notes in ten workspaces. It includes an optional Node.js MCP server that exposes 15 tools over stdio. The tools let Claude Desktop, Claude Code or Codex read the dashboard, create goals and tasks, log habits and record expenses. The MCP server calls only the app's bearer-token /api/v1 HTTP API and never touches the database or credentials. The README is candid about limits: the token has no scopes, there is no app-level rate limiting, and the secret-note flag is only a visibility setting, not encryption.
github.comrepoPublished and added 9 Oct 2026🧠 AI - trhhubsd/ARTEX
ARTEX is an AGPL-3.0 autonomous penetration-testing system with a Go backend and Next.js frontend, backed by PostgreSQL. A planner agent and parallel worker agents share a global asset graph and a per-task exploration graph, with human-in-the-loop approval, a MITM traffic-recording proxy, ScopeSentry asset sync, vulnerability retesting and a shared todolist for multi-step attack chains. The README claims a Baidu agent+ attack-defense challenge win and limits use to local isolated labs.
github.comrepoAdded 27 Oct 2026, published 8 Oct 2026🛡️ Security - chainguard-dev/malcontent
malcontent is Chainguard's open-source malware/supply-chain discovery tool that analyzes binaries (ELF, Mach-O, PE, a.out) and scripting-language source across Linux, macOS and Windows using 14,500+ YARA rules (including third-party rules from Avast, Elastic, FireEye, Mandiant, Nextron and ReversingLabs). Its standout feature is differential analysis ("mal diff"), which compares two versions of a build artifact or OCI image against a known-good baseline to surface newly introduced risky behaviors — the technique the project demonstrates on the 3CX supply-chain compromise by flagging unexpected high-risk changes to libffmpeg. It also supports threshold-based scanning ("mal scan") and unfiltered capability enumeration ("mal analyze"), and is designed to run inside CI/CD pipelines, including air-gapped environments via embedded rules.
github.comrepoAdded 8 Oct 2026🛡️ Security - target/strelka
Strelka is Target's open-source, container-based real-time file scanning system for threat hunting, threat detection, and incident response, built in Go and Python. It runs 50+ scanners (YARA, PE parsing, encrypted ZIP cracking, entropy analysis, etc.) to extract metadata and content from files at enterprise scale, which can feed a SIEM for alerting on suspicious artifacts like an Emotet-laden encrypted ZIP payload.
github.comrepoAdded 8 Oct 2026🛡️ Security - Port of the TypeScript compiler, checker and lsp to Rust, by LLM
ts-rust (npm package tsc-rs) is a from-scratch Rust port of Microsoft's TypeScript compiler/checker/language server (typescript-go), produced almost entirely by LLM coding agents rather than hand-written. The author first spent over $400,000 in API tokens running GPT-5.6 Sol and GPT-6 Astra in long agentic '/goal' loops, which wrote 1.3M lines of Rust but plateaued at ~84% compatibility; switching to Claude Opus 5.5 produced a working version in 10 hours and, after ~$24,000 of further API spend over two weeks, reached 100% compatibility on tested real-world projects while passing all 181,711 ported Go baseline tests. Benchmarks show the Rust port running about 1.6x faster than the Go tsc 7 compiler (though slower than Bun's native `bun check`) across dozens of open-source codebases including VS Code, TanStack Query, Sentry and T3 Code.
github.comrepoPublished and added 8 Oct 2026🧠 AI  The Vulnerable MCP Project — MCP vulnerability database
The Vulnerable MCP Project is a curated, continuously growing database of security vulnerabilities and attack techniques specific to the Model Context Protocol ecosystem. Entries cover concrete CVEs (e.g. CVE-2025-68143/68144/68145 in Anthropic's mcp-server-git), transport-layer SDK flaws (cross-client response leakage, missing DNS rebinding protection in the official TypeScript/Python SDKs), unauthenticated/0.0.0.0-bound servers enabling RCE (MCPJam inspector, MCP Inspector, Grafana MCP), command/path injection in dozens of third-party servers (gemini-mcp-tool, mcp-server-kubernetes, Framelink Figma MCP, Zen MCP, filesystem-mcp), SSRF chains reaching cloud metadata (MarkItDown MCP, mcp-fetch-server), and a large set of AI-specific attacks: tool poisoning, trigger-phrase data exfiltration, prompt injection via GitHub issues, Jira and Google Docs, rug-pull tool mutation, and cross-server tool-name collisions. It functions as the de facto vulnerability registry for the MCP ecosystem, useful for tracking disclosed issues before patching or adopting third-party MCP servers.
 vulnerablemcp.inforepoAdded 6 Oct 2026🛡️ Security
- Microsoft Agent Framework python-1.20.0 release
Release notes for python-1.20.0 of Microsoft's Agent Framework, an open-source agent/workflow orchestration library. This release adds native vector-store connectors for DuckDB, SQL Server and MongoDB plus a TypeSafe AI connector, redesigns Foundry hosting around request-scoped agent factories and sandbox-isolated sessions, adds computer-use support to Responses clients, and ships Magentic manager and handoff-routing improvements for multi-agent orchestrations alongside a large batch of MCP, Bedrock, Gemini, Anthropic and Ollama provider fixes.
github.comrepoAdded 6 Oct 2026🧠 AI - browser-use/jev-ultrafast
jev-ultrafast is an open-source browser automation agent (from Browser Use) that represents each page as an indexed element table and uses a 'TypeSafe' policy to speculatively predict both the next operation (CLICK, TYPE_TEXT, SELECT, SCROLL, WAIT, DONE, BLOCKED) and its target in a single network round trip, only invoking a small LLM (e.g. inception/mercury-2.5 via OpenRouter) to generate text when the operation is TYPE_TEXT. The repo includes a local inspector UI, Chrome automation via a 'Browser Harness' tool, offline tests, and published before/after benchmarks showing a Google Flights search dropping from a median 9.45s to 7.09s and browser protocol calls from 1,092 to 101 across repeated runs.
github.comrepoAdded 6 Oct 2026🧠 AI - Dark Web Informer (@DarkWebInformer) on X
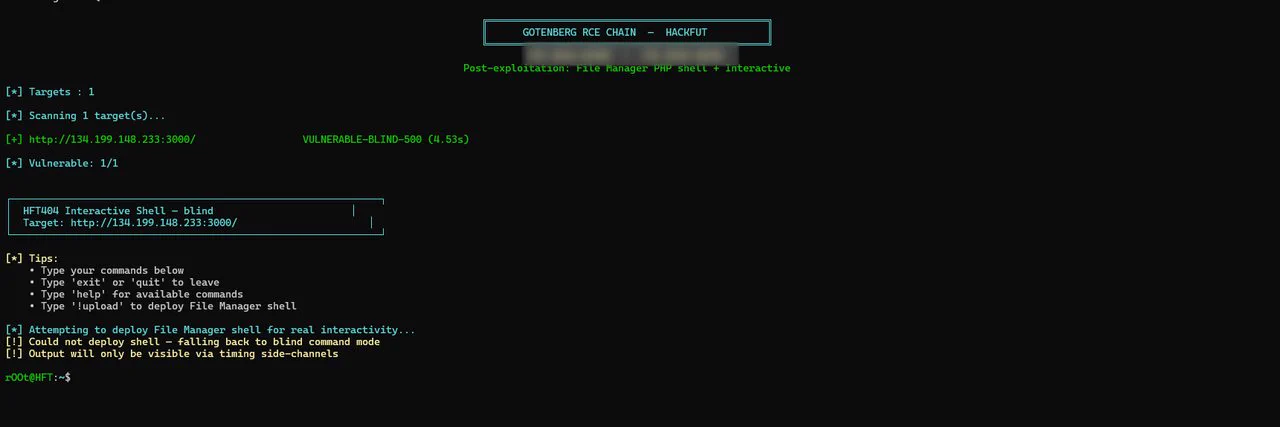
A public PoC chains CVE-2026-42589 and CVE-2026-40281 to achieve unauthenticated remote code execution against Gotenberg (a document/PDF-conversion microservice), abusing metadata injection flaws in the /forms/pdfengines/metadata/write endpoint. The tool supports vulnerability detection, interactive command execution, reverse shell delivery, and multi-target scanning against Gotenberg versions ≤8.30.1 (patched in 8.31.0).
x.comrepoPublished and added 5 Oct 2026🛡️ Security - Sigma r2026-07-01 — 20 new detection rules
GitHub release notes for Sigma r2026-07-01, the open-source detection-rule repository, adding 20 new rules (e.g. LSASS crash via Netlogon buffer overflow CVE-2026-41089, TanStack supply-chain attack indicators for Windows/Linux, RedTail cryptominer user-agent detection, AF_ALG kernel crypto API exploit indicator) and updating/fixing dozens of existing rules for ARM64 binary variants, file-sharing domain IOCs, and WMI-based reconnaissance/persistence detection. It's a routine but substantive update to a widely-used blue-team detection content pack.
github.comrepoAdded 3 Oct 2026🛡️ Security - Show HN: Made an open-source Lego AI generator
ldraw-nova is an open-source agentic pipeline where an LLM agent (tested with models like Claude Opus 5.5 and GPT-6 Astra) takes a build prompt, reads LDraw-building instructions, and produces a plan.json describing a model's geometry. From that plan it writes a Python generator script that, when executed, outputs an LDraw (.mpd) 3D CAD source file, viewable in 3D/VR (Meta Quest 3) or exportable to Blender-editable glTF. The agent uses jev-rerank, a semantic search tool with reranking backed by TypeSafe's Jev System One model, to find suitable LEGO parts and example models, falling back to full-text search without an API key; it also uses headless rendering and collision/gap detection to self-inspect and iterate on designs.
github.comrepoAdded 3 Oct 2026, published 2 Oct 2026🧠 AI - Microsoft Agent Framework — python-1.20.0 release
Release notes for Microsoft's Agent Framework (Python and .NET SDKs), covering versions python-1.16 through python-1.20 and dotnet-1.19 through dotnet-1.23. Changes span native vector-store connectors (MongoDB, Qdrant, PostgreSQL/pgvector, DuckDB, SQL Server, Azure Cosmos DB, Azure AI Search), Foundry hosting redesigns around request-scoped agent factories and durable Invocations, MCP skill/session security hardening (approval binding, security labels, ZIP-only skill archives), Magentic multi-agent orchestration and handoff routing, and checkpoint/replay correctness fixes across workflows.
github.comrepoAdded 2 Oct 2026🧠 AI - Bifrost (Maxim AI) — open-source LLM gateway
Bifrost is an open-source, high-performance LLM gateway (by Maxim AI) that exposes a single OpenAI-compatible API across 23+ providers including OpenAI, Anthropic, AWS Bedrock, Google Vertex, Azure, Cohere, Mistral, and Ollama. It provides automatic failover, load balancing, semantic caching, Model Context Protocol (MCP) tool integration, budget and governance controls, OIDC user provisioning, and Prometheus-based observability, deployable via npx or Docker with claimed sub-15 microsecond overhead at 5,000 RPS. It is positioned as a drop-in replacement requiring only a base-URL change for existing OpenAI, Anthropic, or GenAI SDK code.
github.comrepoAdded 2 Oct 2026🧠 AI - renato-osec/goonfi-v2-decompiled
goonfi-v2-decompiled holds byte-identical reconstructed Rust source for the GoonFi V2 Solana program goonuddtQRrWqqn5nFyczVKaie28f3kDkHWkHtURSLE, as deployed at slot 448984043. The on-chain program was upgraded on 6 October 2026 to fix reported bugs. VERIFY.sh builds with Solana platform-tools v1.48 and compares the result to the deploy transaction's loader buffer writes. The page does not describe the bugs.
github.comrepoAdded 22 Oct 2026, published 2 Oct 2026🛡️ Security - AI-Infra-Guard (A.I.G) — Tencent Zhuque Lab
AI-Infra-Guard (A.I.G) is Tencent Zhuque Lab's open-source AI red-teaming platform combining AI infrastructure vulnerability scanning (2000+ CVE rules covering vLLM, llama.cpp, LangFlow, n8n, MLflow and 145+ other AI components), MCP server/skill security scanning, LLM API poisoning detection, and multi-turn jailbreak evaluation (Many-Shot, PAIR, GOAT, ActorAttack). It ships CLI tools (skill-scan, mcp-scan, agent-scan), a Docker-deployed web UI, and has produced original research including FORGE-Bench (loss-of-control benchmark), RogueHandoff-20, and SkillJack (persistent skill backdoors), with talks at Black Hat Europe 2025 on MCP security.
github.comrepoAdded 30 Sep 2026🛡️ Security - Andrea (Drego) Draghetti 👨🏻💻 🎣 (@AndreaDraghetti) on X
Tosint v1.0.0 is an open-source Telegram OSINT tool for analyzing bots and chats, exporting message history and media. The new release adds richer JSONL metadata output, optional SHA-256 hashing of exported media, bot/user authentication support, and an automatic fallback from MTProto-based history retrieval to ID-scan mode when dealing with restricted chats.
x.comrepoAdded 2 Oct 2026, published 30 Sep 2026🛡️ Security - rehan-remade/universal-modder
universal-modder is a set of Agent Skills, a CLI (um) and a shared knowledge base (field notes in knowledge/) that let AI coding agents such as Claude Code, Codex, Gemini CLI, Cursor, GitHub Copilot and OpenCode find a PC game's engine, reverse-engineer its code, build a working mod, generate art/3D/sound assets via the fal MCP server (or a local ComfyUI server), test the mod in the running game, and write a field note for the next agent. It ships worked examples — a weapon/boss pack for Terraria via tModLoader, a new civilization for Age of Empires II DE, and a real-time Minecraft-inside-GTA-V passthrough mod — each documented with a field note of exact versions, routes and gotchas, and agents can open pull requests to grow the shared knowledge base.
github.comrepoAdded 6 Oct 2026, published 30 Sep 2026🧠 AI - NVIDIA OpenShell — secure runtime for autonomous AI agent fleets
OpenShell is NVIDIA's open-source runtime for running fleets of autonomous AI agents with restricted, policy-governed access to files, system calls, network, and credentials. It enforces policy at the kernel level inside isolated sandboxes (per-agent, with Docker/Podman/virtualization backends) and uses formal verification to flag risky policy changes — such as an agent gaining a new host or API access with credentials — before they take effect, so changes can wait for human review. It ships a CLI, a gateway control plane, Kubernetes/Helm deployment, and installable agent skills for writing and debugging sandbox policies.
github.comrepoAdded 29 Sep 2026🧠 AI - garak v0.17.0 — LLM vulnerability scanner release
Release notes for garak v0.17.0, NVIDIA's open-source LLM vulnerability scanner used for red-teaming and probing models for jailbreaks, prompt injection, data leakage and other failure modes. The release adds an EU AI Act risk-category mapping to tag and group probe results, plus fixes to detectors (agent_breaker judge verdict validation, packagehallucination import parsing, MarkdownExfilContent divide-by-zero, TriggerListDetector alignment) and probes (badchars ASCII selection, Markdown exfiltration link templates), along with Ollama generator improvements and dropped Python 3.10 support in favor of 3.13.
github.comrepoAdded 29 Sep 2026🛡️ Security - NVIDIA OpenShell — secure runtime for autonomous AI agent fleets
OpenShell is NVIDIA's open-source runtime for running fleets of autonomous AI agents in isolated sandboxes, enforcing per-agent policies on filesystem, syscall, and network access at the kernel level and injecting credentials only for approved endpoints. Policy changes go through a formal-verification step (an 'advisor'/'prover') that flags newly granted risky access, such as a new host reachable with credentials, before it's applied, and it deploys via Docker/Podman/host virtualization or Kubernetes with Helm.
github.comrepoAdded 29 Sep 2026🛡️ Security  Ternary-Bonsai-2-27B: 27B model compressed to ~1.75 bits/weight, 98.2% of FP16 quality retained
Ternary-Bonsai-2-27B is a 27B-parameter reasoning model (built on Qwen3.8-27B) quantized to true ternary weights ({-1,0,+1}) at ~1.72 bits/weight, shrinking it from ~54GB FP16 to ~5.95GB while retaining 98.2% of FP16 benchmark quality (84.78 vs the conventional sub-4-bit IQ2_XXS build's 72.59). It uses a Hadamard-rotated weight basis and ships two GGUF packing formats (PTQ1_0 dense trits, PQ2_0 2-bit slots) that require a custom llama.cpp/MLX kernel fork since stock llama.cpp cannot decode them correctly. The card includes per-category benchmark breakdowns (math, coding, agentic tool calling), cross-platform throughput/power measurements (Apple M5 Pro/Max, RTX 5090, L4, H100/A100/Blackwell), and an "intelligence density" metric comparing capability retained per GB against FP16 and other quantizations.
huggingface.corepoAdded 29 Sep 2026🧠 AI- Uncensored and Offensive Security AI Models Benchmark
A GitHub README curating open-weight "uncensored" and security-fine-tuned LLMs (e.g. WhiteRabbitNeo's DeepHat V2, BugTraceAI-CORE, CYBER-FROST, CyberPal2.0, Lily-Cybersecurity-7B, Dolphin-Llama3-8B, Wizard-Vicuna-13B-Uncensored, huihui-ai's abliterated Qwen variants) with HuggingFace download links, quantization formats (GGUF, FP8, Q4_K_M, Q6_K), and training techniques used (SFT, QLoRA, DPO, abliteration, MoE/MTP architectures). It also includes a glossary explaining abliteration (orthogonalizing the refusal direction out of the residual stream, per Arditi et al. 2024) and references benchmarks like CyberBench and TrustedSec's LLM Attack Benchmark, making it a practical reference for anyone sourcing or deploying refusal-removed models.
github.comrepoAdded 2 Oct 2026, published 29 Sep 2026🧠 AI - dagoSte/squadra
Squadra (version 3.11.0) is an MIT-licensed Python 3.12+ tool that coordinates several Claude Code, Codex and interactive Cursor windows on one project through a shared local registry. It records tasks, acknowledgements, source-bound proofs and independent reviews by a window that did not write the code. A local dashboard shows progress, per-window token usage and model-balance suggestions, and community plugins extend it. The page was truncated, so later sections are not covered.
github.comrepoAdded 27 Oct 2026, published 28 Sep 2026🧠 AI - Adversarial-Detection-Engineering/adeskills
adeskills is a working knowledge base for "Adversarial Detection Engineering" (ADE), a taxonomy of four categories and 16 subcategories of detection-logic bugs (e.g. Reformatting in Actions, Omit Alternatives, Context Development, Logic Manipulation) that explain why a SIEM/EDR/XDR rule fails to catch what it intends to. It ships 38 worked technique files with vulnerable/hardened rule examples and detection-layer guidance, a cross-platform bug-pattern catalog, a pre-engagement scoping checklist, and a Redamon-packaged skill (ade_scoper), all grounded in analysis of real public rulesets from Sigma, Elastic Security, and Microsoft Sentinel. It's explicitly scoped for defensive detection engineering and purple-team rule hardening, with several files documenting real vendor-rule weaknesses.
github.comrepoAdded 2 Oct 2026, published 27 Sep 2026🛡️ Security - zhuyansen/awesome-claude-video-skills
Awesome-list repository cataloguing 183 open-source 'skills' and toolkits that let Claude Code, Codex and other coding agents generate or edit video: rendering frameworks like HyperFrames and Remotion, motion graphics, explainer/promo video generators, short-form editors, digital avatars and music videos. Each entry is read and security-graded by a companion service (Agent Skills Hub / agentskillshub.top), with a machine-readable JSON feed and category breakdowns (frameworks, promos, explainers, editing, shorts, avatars, animation, motion graphics, scripts, music videos).
github.comrepoAdded 29 Sep 2026, published 27 Sep 2026🧠 AI - Agent Control Standard (ACS)
Agent Control Standard (ACS) is an OWASP GenAI Security Project specification that lets a separate Guardian Agent inspect an AI agent's proposed actions before they execute and return allow/deny/modify/ask/defer over an authenticated JSON-RPC wire, with OpenTelemetry/OCSF audit trails and a CycloneDX/SPDX/SWID AgBOM inventory. The reference implementation runs Microsoft's Agent Governance Toolkit (AGT) behind the ACS contract with Bun, including host shims for Claude Code and OpenCode, and demonstrably denies a destructive `rm -rf /` command from a live coding-agent session while allowing benign ones. The project is explicit about current gaps — the wire is unauthenticated (issue #70) and the reference Guardian fails open by default (issues #32/#37) — and only 2 of 16 lifecycle hooks are evaluated live in v0.1.0.
github.comrepoAdded 26 Sep 2026🛡️ Security - garak v0.17.0 — adds EU AI Act risk-category mapping
garak is NVIDIA's open-source LLM vulnerability scanner that runs probes/detectors for jailbreaks, prompt injection, PII leakage, package hallucination, markdown exfiltration and more against LLM targets. This v0.17.0 release adds a new EU AI Act risk-category mapping to tag and group probe results by the Act's risk categories, alongside fixes to the agent_breaker judge, markdown-exfiltration detectors, Ollama auth/generation support, and dropped Python 3.10 in favor of 3.13 support.
github.comrepoAdded 26 Sep 2026🛡️ Security - graygnatconsole/mcp-audit-tool
mcp-audit-tool is a dependency-light Python CLI that statically scans Claude Desktop, Cursor, Windsurf, Cline, Zed, and VS Code MCP configuration files for security issues, including hardcoded secrets, unpinned/rug-pull packages, pipe-to-shell installers, tool-poisoning via hidden instructions in tool descriptions, filesystem servers rooted at '/', and unauthenticated plaintext HTTP MCP endpoints. It auto-discovers configs across macOS/Linux/Windows, produces a security score/grade plus SARIF 2.1.0 output for GitHub Code Scanning, and is built around the OWASP MCP Top 10 categories with a CI/CD example that fails builds on severity thresholds. The roadmap adds live server probing over stdio/SSE for runtime rug-pull detection and an ML-based prompt-injection classifier for tool descriptions.
github.comrepoPublished and added 26 Sep 2026🛡️ Security - google/ax — declarative agentic orchestration runtime
AX is Google's declarative orchestrator for running large numbers of autonomous agent workloads on Kubernetes, built on top of "Agent Substrate" for sandboxed execution. Agents are declared via YAML manifests (Task, Workspace, Model) similar to kubectl, and applied with an `ax` CLI that supports apply/get/watch/ssh/suspend/resume, treating agent runs as a distinct workload type distinct from stateless services or batch jobs.
github.comrepoAdded 26 Sep 2026🧠 AI - Hindsight — Agent Memory That Learns
Hindsight is an open-source agent memory system (MIT-licensed, self-hostable via Docker/Helm or usable as Hindsight Cloud) that goes beyond RAG-style recall by having agents learn through consolidated observations and mental models built from retained facts and experiences. It exposes retain/recall/reflect operations, a built-in MCP server per memory bank, Python/Node/Go/CLI clients, an LLM-wrapper for drop-in memory on OpenAI/Anthropic calls, and reports state-of-the-art results on the LongMemEval long-term memory benchmark, independently reproduced by Virginia Tech's Sanghani Center and The Washington Post.
github.comrepoAdded 26 Sep 2026🧠 AI - git-pkgs — dependency history & supply-chain analysis for git repos
git-pkgs is a Go rewrite of a Ruby tool that adds a git subcommand for tracking dependency changes across a repository's history, indexing manifests/lockfiles from 36+ package managers (npm, RubyGems, Cargo, PyPI, Maven, Composer, Go modules, etc.) into a local SQLite database. Beyond history/blame/diff, it offers supply-chain security commands: `vulns` (OSV-based CVE scanning with SARIF output for GitHub code scanning, plus blame/praise/exposure for remediation metrics), `licenses` (with drift detection and CI-friendly exit codes), `deprecated`, `provenance` (trusted-publishing/attestation checks), `integrity` (lockfile hash drift detection), `maintainers`/`health` (via ecosyste.ms metadata), and `sbom` export in CycloneDX/SPDX. It also supports a dependency-aware `bisect` to find when a vulnerability, license change, or capability (e.g. network access) was introduced, and ships GitHub Actions for CI integration.
github.comrepoAdded 25 Sep 2026🛡️ Security - yetone/magpie
magpie is a cross-platform menu bar app, TUI and CLI that lets you view and switch the model each installed AI coding agent (Claude Code, Codex, Gemini CLI, OpenCode, Cursor, Copilot CLI, Goose, Pi, etc.) is configured to use, editing each agent's config file surgically without disturbing comments or formatting. It runs a local gateway (127.0.0.1:3425) that translates between OpenAI Chat Completions, OpenAI Responses and Anthropic Messages APIs so every agent can point at one endpoint and use any provider's models, including routing groups that spread requests across multiple keys/subscriptions with configurable routing strategies (smart, order, rotate, usage). It can also reuse existing subscriptions (Claude Code, Codex/ChatGPT, Copilot, Devin, Gemini CLI) as providers for other agents without exposing or copying credentials, and supports encrypted profile backup/restore.
github.comrepoAdded 26 Sep 2026, published 23 Sep 2026🧠 AI - https://github.com/akha-security/akca
AKCA is an open-source, Go-based Dynamic Application Security Testing (DAST) scanner that combines HTTP and headless-browser crawling, JavaScript/AST analysis, API spec import (OpenAPI, GraphQL, gRPC, etc.), and adaptive active testing across a very broad set of vulnerability classes including SQL injection, XSS, SSRF, IDOR/BOLA, SSTI, JWT/OAuth flaws, race conditions, and cloud/CI exposure. It emphasizes evidence-oriented verification — replaying promising signals against baselines, negative controls, and OAST callbacks before promoting them to findings — and exports Burp-style HTTP evidence in HTML, JSON, CSV, Markdown, and SARIF reports. Positioned as a transparent, single-developer alternative inspired by but not claiming parity with Acunetix, Invicti/Netsparker, or Burp Suite Professional.
github.comrepoAdded 2 Oct 2026, published 23 Sep 2026🛡️ Security - shai-hulud-detect: multi-ecosystem npm/PyPI/Composer/Crates/Go/Hex/RubyGems supply-chain worm scanner
shai-hulud-detect is a dependency-free Bash scanner that checks projects against a 5,782-entry list of compromised npm, PyPI, Composer, Crates, Go, Hex, and RubyGems package versions, plus content-pattern indicators of compromise (malicious file hashes, C2 domains, dead-man's-switch artifacts, forged commits, suspicious lifecycle hooks) tied to the Shai-Hulud supply-chain attack waves. It supports single-project and bulk scanning, CI-friendly exit codes, JSON/log output for pipeline gating, and a --check-host mode to detect the May 2026 gh-token-monitor/kitty-monitor persistence daemons that wipe hosts if their monitored GitHub token is revoked (with a documented safe remediation order). Detection is read-only; new package entries are sourced from named threat-research firms (Socket, StepSecurity, Aikido, Snyk, JFrog, Wiz, Semgrep, SafeDep, GitGuardian, OX Security) and cited in PRs.
github.comrepoAdded 23 Sep 2026🛡️ Security - nealbridges/VulnHunter
VulnHunter is a maintained fork of Capital One's open-source agentic security scanner, reworked to run on any agent harness (Claude Code, Codex, Grok/OpenCode) instead of being Claude-Code-specific. The fork's distinguishing work is engineering, not security findings: portable "skill" prompt files with an explicit environment contract, an installer that fails loudly instead of guessing paths, Docker-based sandboxed exploit validation, and a benchmark harness that ran six full scans of one production Go service across five model/harness stacks, finding that result counts swung from 3 to 42 findings depending on how rigorously exploits were validated. It ships three composable skills (/vulnhunt, /vulnhunter-fix, /vulnhunt-fix-verify), a headless batch-runner (harness/), and a deterministic manifest-writing CLI (vh).
github.comrepoAdded 6 Oct 2026, published 22 Sep 2026🧠 AI - nealbridges/VulnHunter
A maintained, harness-portable fork of Capital One's open-source VulnHunter — an agentic AI tool that performs attacker-first forward analysis on source code to find exploitable vulnerabilities, falsify weak findings, and produce evidence-backed PoCs rather than pattern-matched SAST alerts. This fork adds containerized (Docker-based) exploit validation, measured-impact PoCs (rows leaked, amplification factor, etc.), and portability across agent harnesses (Claude Code, Codex, Grok, etc.) via environment-contract prompt files, plus an unattended operator (vulnhunter-run) and batch-scanning/benchmark harness tested against OWASP NodeGoat, Juice Shop, and WebGoat.
github.comrepoAdded 6 Oct 2026, published 22 Sep 2026🛡️ Security - yibie/jev-engineering-zh
A Chinese translation (with original source notes) of a design essay synthesizing TypeSafe founder Diogo Almeida's notes on 'Jev,' a typed decision model that drives a coding-agent harness. It argues coding agents are simple loops whose real leverage lies in how context is assembled each turn, and works through six problems inherited from KV-cache-driven, append-only context design: costly model routing, tool-schema bloat, lossy compaction, rare sub-agents, destructive session restarts, and the built-in-capabilities tradeoff. It proposes fixes including query-aware context scoring/visibility tiers, cost-aware routing that accounts for cache reprocessing, tiered tool disclosure, conditional AGENTS.md loading, and shared read-only background retrieval.
github.comrepoAdded 26 Sep 2026, published 22 Sep 2026🧠 AI - Supply Chain Firewall (Datadog)
Supply Chain Firewall (SCFW) is a Datadog-built CLI that wraps npm, pip, and poetry commands to inspect every package target against known-malicious/compromised package datasets (the open-source malicious-software-packages-dataset and OSV.dev) before installation proceeds, blocking or warning on hits. It ships as a single Go binary, can be aliased transparently into a developer's shell, and optionally reports run outcomes and enforces centralized allow/block policies through Datadog Code Security across a fleet, sending only package metadata (never source code) to Datadog.
github.comrepoAdded 22 Sep 2026🛡️ Security - SnailSploit/Claude-Red
claude-red is a GitHub library of structured SKILL.md files for the Claude Skills system, each priming Claude with expert-level offensive-security methodology for a specific attack surface (SQL injection, shellcode, EDR evasion, ADCS abuse, wireless, IoT, cloud, mobile, fuzzing, etc.). Skills load on-demand from conversational triggers so context isn't spent on unused domains, and can be installed wholesale, per-category via sparse-checkout, or pasted directly into a system prompt. It's aimed at authorized red-team engagements, bug bounty triage, CTF prep, and operator training, building on Sahar Shlichov's offensive checklist collections.
github.comrepoAdded 21 Sep 2026🛡️ Security - Gihchathur/kubemotion
KubeMotion is a browser-only visualizer that turns raw Kubernetes YAML or a packaged Helm chart (.tgz) into an interactive, Argo CD-style dependency graph without ever connecting to a live cluster or executing Helm. Beyond visualization it runs rule-based checks for common deployment problems — missing probes, incomplete containers, missing selectors, missing service accounts, and mutable image tags — surfaced per-resource in an inspector panel, and can export the resulting architecture as a Mermaid diagram. Built with React, TypeScript, Vite, React Flow and CodeMirror; explicitly a read-only, credential-free tool for reviewing manifests/charts before they're applied.
github.comrepoAdded 21 Sep 2026🛡️ Security - ossf/criticality_score
criticality_score is an OpenSSF tool that computes a 0-1 criticality score for open source projects (based on an algorithm by Rob Pike), using signals like contributor count, commit frequency, dependents count, and org diversity to identify projects the ecosystem critically depends on. It ships a CLI, config files for tuning scoring weights, and companion tools (enumerate_github, collect_signals, scorer) for large-scale data collection; the project's GCP-hosted BigQuery/GCS datasets will be discontinued after 2026-08-29, with data moving to a static data directory.
github.comrepoAdded 21 Sep 2026🛡️ Security - sno-ai/sno-station
Sno Station is an open-source (Apache-2.0) local workstation that coordinates multiple AI agents (Claude Code, Codex, OpenClaw) as a 'Duo': they share an encrypted on-disk memory store, hand off tasks when one hits a rate limit, peer-review each other's work, and run a nightly self-improvement loop that proposes edits to their own skill files based on session history. It reports results on the Memora benchmark (FAMA/FAA metrics for forgetting-aware long-term memory) and cites Karpathy's 'LLM Wiki' and Google's WikiSkill as design inspirations.
github.comrepoAdded 26 Sep 2026, published 19 Sep 2026🧠 AI - MichaelKinsy/PiG
PiG reimplements Pi — a minimal, extensible terminal coding agent — as a single native Go binary with no Node.js dependency, while remaining behaviorally pinned to a specific Pi release (0.87.1) and running Pi's TypeScript extensions unchanged. It adds a multi-language extension host (Go, Rust, Python, Node), a "Piglet" mechanism for bundling extensions/skills/prompts into a named shareable agent, and a formal parity-tracking process (PORT_MAP.md, DIVERGENCES.md, coverage reports) that documents every intentional divergence from the upstream Pi reference implementation.
github.comrepoAdded 27 Sep 2026, published 17 Sep 2026🧠 AI - Copy Fail (CVE-2026-31431): 9-year-old Linux kernel LPE found by Theori's Xint Code
A GitHub repository from Theori's Xint Code team detailing CVE-2026-31431, a Linux kernel local privilege escalation bug ("Copy Fail") that had gone undetected for roughly nine years. The researchers confirmed exploitability across current production kernels including Ubuntu 24.04 LTS (6.17.0-1007-aws), Amazon Linux 2023 (6.18.8-9.213.amzn2023), RHEL 10.1 (6.12.0-124.45.1.el10_1), and SUSE 16 (6.12.0-160000.9-default).
github.comrepoAdded 17 Sep 2026🛡️ Security - ThreatIntel-Aggregator
ThreatIntel-Aggregator is a self-hosted FastAPI/Next.js platform that polls 60+ tiered security RSS feeds (CISA, Talos, Unit42, etc.), runs AI triage to score severity and tag MITRE ATT&CK TTPs, extracts IOCs/CVEs, and correlates findings against a RunZero asset inventory to surface org-level exposure. Its Detections module goes further: it catalogs AI-generated or locally-imported detection rules (KQL/Sigma/YARA/Suricata/SPL), statically validates them, runs AI-driven MITRE alignment checks against technique coverage, tracks detection "rot," and can sync Hunts/Analytics Rules to a live Microsoft Sentinel workspace. It's designed to run standalone with zero cloud dependency or fully integrated with Azure/Entra/Sentinel, with all storage in Postgres and auth via Entra SSO or a local API key.
github.comrepoAdded 22 Sep 2026, published 17 Sep 2026🛡️ Security - AI Agent Hacking Writeups
A GitHub-hosted, CC0-licensed index of 281 public writeups on attacks against AI agents, organized into six categories: indirect prompt injection, direct prompt injection/jailbreaks/guardrail bypass, MCP and agent tooling, AI platform/infrastructure bugs, classic web bugs in AI product surfaces, and AI used as an attacker's tool. Entries span 2021-2026 and include major disclosures like GeminiJack, ForcedLeak, Clinejection, CVE-2025-53773 (GitHub Copilot RCE), and dozens of Johann Rehberger/PromptArmor/qual1a writeups covering exfiltration, MCP OAuth flaws, and coding-agent sandbox escapes. Comes with an accompanying blog post "How to Hack AI Agents" and a scripted links.txt for automation.
github.comrepoAdded 22 Sep 2026, published 17 Sep 2026🛡️ Security - Mapika/decider
Decider is an open reproduction of TypeSafe AI's System One (Jev) model class: instead of generating text, it reads a state plus a set of typed questions (Choice, Score, or Noul/yes-probability) and returns a calibrated probability distribution for each in one forward pass, with no decoding or parsing. The repo ships 2B/4B/12B and a 35B mixture-of-experts checkpoint (built on Qwen3.5 and Gemma-4 base models), trained on roughly 95 public datasets plus teacher-labelled data, with per-type temperature calibration, GGUF/llama.cpp and vLLM serving paths, an MPS/Apple Silicon port, and a community Snapdragon X Elite NPU port. It benchmarks against TypeSafe's Jev on JevBench and the Decision Index, documenting where it closes the gap (language, tools, retrieval) and where it lags (knowledge-heavy MMLU/GSM8K/GPQA tasks and calibration on hard items).
github.comrepoAdded 2 Oct 2026, published 16 Sep 2026🧠 AI - OpenHunterAI
OpenHunterAI is a self-hosted, alpha-stage AI red-teaming workspace that applies attacker-style reasoning to web, API, and LLM application security testing against verified, in-scope public targets. It runs locally via Docker/Node.js, orchestrates bounded testing (scope lock → surface mapping → baseline → hypothesis testing → evidence gating → report/retest) through Go workers over NATS, and ships adapters for browser inspection, OWASP ZAP, and Nuclei, with separate OpenHack and Strix runtime integrations and an agent skill for Claude Code/Codex/Gemini CLI/Grok.
github.comrepoAdded 22 Sep 2026, published 15 Sep 2026🛡️ Security - agent-egress-bench
Agent Egress Bench is an open, tool-neutral benchmark maintained by PipeLab (makers of Pipelock) that tests whether products mediating an AI agent's outbound traffic — proxies, egress firewalls, MCP wrappers, agent gateways — actually catch exfiltration attempts caused by prompt injection or misalignment, rather than testing the underlying model itself (that's left to AgentDojo, InjecAgent, CyberSecEval, AgentHarm, ASB). It ships a reproducible Go runner with a proxy/WebSocket/MCP/A2A adapter contract, an offline validator, DSSE-signed evidence bundles, and a CI-runnable GitHub Action, and separates containment from false-positive rate as two distinct scored axes with immutable case IDs and OWASP Agentic Top 10/MITRE ATT&CK mappings. Its governance explicitly permits third parties to publish results unfavorable to the maintainer's own Pipelock product.
github.comrepoAdded 12 Sep 2026🛡️ Security - AWSHound — AWS BloodHound OpenGraph Collector
AWSHound is a Go CLI/container tool that collects AWS IAM and authorization data across profiles, config-file opt-ins, or an entire AWS Organization (via cross-account role assumption), and outputs a BloodHound OpenGraph for attack-path analysis. It supports phased collection with on-disk artifacts, offline graph building from previously collected data, and safeguards like --max-api-requests and --max-api-requests-per-minute to bound AWS API traffic during collection.
github.comrepoAdded 8 Sep 2026🛡️ Security - punkpeye/awesome-remote-mcp-servers
Awesome Remote MCP Servers is a curated GitHub list of hosted Model Context Protocol servers that you connect to by URL, with no local install. Entries are listed only after the endpoint answers an MCP initialize handshake. It explains local versus remote servers, shows connection examples for Claude Code and mcp.json, marks auth as none, API key or OAuth, and groups servers into about 40 categories.
github.comrepoAdded 2 Nov 2026, published 8 Sep 2026🧠 AI - vet (SafeDep)
vet is an open-source CLI (from SafeDep) that scans package manifests, SBOMs, container images, and source repos across npm, PyPI, Maven, Go, RubyGems, Cargo, and Packagist to surface vulnerabilities, malicious packages, and license/quality issues. It cuts through CVE noise by analyzing actual code-usage evidence, queries SafeDep Cloud's threat-intelligence database for real-time malware detection (e.g. flagged packages like express-cookie-parser, eslint-config-airbnb-compat), and lets teams enforce security/license/OpenSSF-Scorecard policies as CEL expressions in CI/CD via SARIF/JSON/Markdown reporting.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - PlamenTSV/plamen
Plamen is an open-source Python orchestrator that drives 18-100 Claude Code or OpenAI Codex CLI agents across 40+ phases to autonomously audit smart contracts (EVM/Solidity, Solana/Anchor, Aptos Move, Sui Move, Soroban, DAML/Canton) and L1 node-client infrastructure (Go/Rust consensus, p2p, mempool code), producing a severity-tiered AUDIT_REPORT.md with verified proof-of-concept exploits for each finding. It integrates MCP servers for Slither, ChromaDB and Solodit, ingests vulnerability corpora from Solodit, DeFiHackLabs and Immunefi to ground findings, and runs a PTY-supervised worker-pool architecture with checkpoint/resume, artifact-based completion gating, and a dedicated L1 mode with consensus-invariant and network-surface depth agents.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - andyrewlee/awesome-agent-orchestrators
A curated GitHub list cataloguing open-source and source-available tools for orchestrating AI coding agents, organized into categories: terminal multiplexers/TUIs (tmux+worktree managers like claude-squad, amux, agent-manager), desktop/web parallel-session apps (Ghostex, Tempest, Vicoa), multi-agent swarms with inter-agent coordination (crewAI, gastown, loki-mode), autonomous loop runners (Ralph Wiggum-style loops like ralph-orchestrator, bernstein), issue/board-driven task runners (cyrus, open-swe, claude-code-action), infrastructure/control-plane primitives (Concord MCP, Agent Messaging Protocol), and always-on personal assistants (openclaw, rowboat). It covers dozens of tools working with Claude Code, Codex, Gemini CLI, OpenCode, and other agent CLIs, plus a watchlist of stalled projects. Useful as a map of the fast-moving agent-orchestration tooling landscape as of mid-2026.
github.comrepoAdded 23 Sep 2026, published 7 Sep 2026🧠 AI - ForgeGuardian
ForgeGuardian is an open-source (Apache 2.0) supply chain security scanner covering 9 package ecosystems (npm, PyPI, Go, Maven, RubyGems, Cargo, NuGet, Hugging Face, GitHub Actions) via 8 concurrent scan engines and 223+ built-in malicious-package detection signatures. It runs fully offline/local-first, offers a CLI (fgctl) and self-hosted SOC-style dashboard, generates CycloneDX/SPDX SBOMs, supports Sigstore keyless signing and provenance tracking, policy-as-code rules, dependency topology/attack-surface mapping, drift detection with auto-quarantine, and SARIF output for GitHub Actions CI integration, plus optional AI-powered advisory/patch-agent triage.
github.comrepoPublished and added 5 Sep 2026🛡️ Security - OWASP OASIS
OWASP OASIS is a proposed community project that operationalizes turning automated vulnerability/fix-generation tool output into human-validated pull requests submitted upstream to open source projects. It defines a full lifecycle (intake, weighted validator review with accept/reject/modify/duplicate decisions, OWASP adoption, ephemeral working forks, upstream submission) plus roles (project owners, validators, maintainer liaisons, automation operators) and outcome metrics like upstream acceptance rate. The GitHub repo lays out governance via a validators.yml credibility file, CODEOWNERS-gated scoring, and GitHub Projects/issue templates to run the whole thing without custom tooling.
github.comrepoPublished and added 5 Sep 2026🛡️ Security - Numbat
Numbat is a Go-based, single-binary endpoint agent from Perplexity AI that gives visibility into AI coding-agent activity (Claude Code, Codex, OpenClaw, and other CLI/IDE/gateway agents) by capturing events through local hooks, OTLP/HTTP logs, and on-disk session artifacts. It normalizes activity into one event model, evaluates it with a local CEL rule engine (including multi-step sequence rules like secret-read-then-egress), and can optionally block matched actions via synchronous pre-action hooks (deny/monitor decisions), with case bundles and SHA-256 manifests for forensic reconstruction. Example built-in rules detect cloud-metadata SSRF requests (169.254.169.254) and credential-exfiltration chains, mapped to MITRE ATT&CK technique tags.
github.comrepoPublished and added 5 Sep 2026🛡️ Security - iamzulx/crypto-rag
crypto-rag is an Indonesian-language CLI crypto assistant that pairs a static knowledge-base RAG pipeline with live market data tool calls, built on the principle that volatile numbers (price, funding rate, TVL, sentiment) must never be embedded in the vector store since they go stale instantly. It implements hybrid retrieval (BM25 keyword search + FAISS dense embeddings fused via Reciprocal Rank Fusion) over a 146-topic knowledge corpus, an optional cross-encoder reranker, and an intent router that dispatches price/derivatives/on-chain/sentiment queries to live sources (Binance, DefiLlama, Fear & Greed Index) versus concept questions to the corpus. A tool-calling agent handles multi-step queries, and an OpenAI-compatible LLM synthesis layer (works with StepFun, OpenAI, Groq, LM Studio, Ollama) grounds answers with citations and falls back to extractive answers when no LLM is configured.
github.comrepoAdded 2 Oct 2026, published 5 Sep 2026🧠 AI - N4darae/shrt
shrt is a Go command-line tool for regression testing RPC backends. Agents, such as Claude Code through a SKILL.md skill, write per-domain contract overlays, and the planner composes RPC chains that probe boundaries, other roles, missing tokens and read-backs after writes. The tool runs and verifies chains against approved runs, and a gate command checks every new release. A person must approve any chain before it becomes a baseline.
github.comrepoAdded 23 Oct 2026, published 3 Sep 2026🧠 AI - h5i-dev/awesome-ai-agent-incidents
A curated GitHub corpus tracking real-world security incidents, CVEs, attack techniques, and defensive tools specific to autonomous AI agents — spanning prompt injection/goal hijacking, MCP client-side tool-metadata poisoning, the "Promptware Kill Chain" multi-stage attack model, MITRE ATLAS agentic techniques, and the OWASP Top 10 for Agentic Applications. It also documents the OpenClaw/ClawHub supply-chain incident (1,184 malicious skills confirmed by Antiy CERT) and links defensive projects like OWASP Agent Memory Guard for LangChain/LlamaIndex agent memory protection.
github.comrepoAdded 3 Sep 2026🛡️ Security - Agenta-AI/awesome-ai-agent-platforms
A curated, CC0-licensed GitHub list cataloguing open-source AI agent platforms across five categories: persistent AI coworkers (Agent Zero, Agenta, LibreChat, LobeChat, Open WebUI, OpenClaw), developer agent frameworks (CrewAI, LangGraph, LlamaIndex, Haystack, Langflow, Letta, Agno, Pydantic AI, OpenAI Agents SDK), workflow/automation runtimes (n8n, Temporal, Prefect, Dagster, Apache Airflow, Windmill), browser agents (Browser Use, Skyvern), and coding agents (Aider, Cline, Goose, OpenHands, Open Interpreter). Each entry states a factual one-line description plus its license and hosting model, with selection criteria requiring an active repo, a usable product, and verifiable licensing — companion comparison table hosted at aiagentplatforms.dev.
github.comrepoAdded 30 Sep 2026, published 2 Sep 2026🧠 AI - cyanheads/osv-advisory-mcp-server
osv-advisory-mcp-server is an MCP server that queries the OSV.dev vulnerability database, offering single-package version checks, batch audits of up to 1000 {name, ecosystem, version} tuples for SBOM/lockfile triage, and full advisory record fetch by OSV ID (GHSA/PYSEC/RUSTSEC/GO/DSA/DLA/CVE prefixes). It surfaces CVE aliases, CVSS vectors, derived severity labels, and CWE IDs, and is designed to chain into a companion nist-nvd-mcp-server for CVSS base scores, EPSS probability, and CISA KEV status. It ships as a keyless, no-API-key tool runnable via STDIO or Streamable HTTP, with a public hosted instance and Bun/npx/Docker install paths.
github.comrepoAdded 1 Sep 2026🛡️ Security - Nehanth/pooled
Pooled runs one open model (Qwen 3.6 35B MoE, a 27B dense hybrid, smaller Qwen3/SmolLM) across devices in a browser "room". Each tab holds a slice of layers and runs them on its own GPU with custom WGSL kernels. Hidden states pass over WebRTC, and speculative decoding is checked against plain decoding by golden tests. It also ships a Code-mode agent loop with a sandboxed preview, and an npx CLI bridge (@pooled/cli) that exposes the room as an OpenAI Chat Completions/Responses and Anthropic Messages endpoint with grammar-constrained tool calling, so Codex CLI, Claude Code and opencode can use it. The README includes latency-injected benchmarks, a comparison with exo, Petals, llama.cpp RPC and WebLLM, and a threat model.
github.comrepoAdded 16 Oct 2026, published 1 Sep 2026🧠 AI - age
age is a simple, modern file encryption tool, format, and Go library by Filippo Valsorda and @benjojo, offering small explicit keys, no config options, UNIX-style composability, and now built-in hybrid post-quantum encryption (ML-KEM + X25519) as of v1.3.0. It supports multiple recipients, passphrase encryption, SSH key (ed25519/rsa) recipients/identities, hardware tokens via age-plugin-yubikey, and an age-inspect command to view encrypted-file metadata without decrypting.
github.comrepoAdded 3 Sep 2026, published 31 Aug 2026🛡️ Security - numasec
numasec is an open-source AI security agent that runs in the terminal, wrapping a user-chosen LLM (OpenAI, Anthropic, Google, Bedrock, Ollama, etc.) with an operation kernel that tracks target scope, runbooks, findings, evidence, replay, and reports across a security engagement. It orchestrates local tools such as nmap, sqlmap, ffuf, gobuster, nikto, nuclei, trivy, and checksec, and is aimed primarily at authorized AppSec triage and Pentest workflows, with OSINT, CTF, and cloud surfaces marked as less mature.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - DataSentry
DataSentry is a Claude Code plugin that redacts secrets (AWS keys, tokens, credentials) from tool outputs before they enter the model's context window, using deterministic hooks rather than model instructions, and blocks prompts that contain live credentials. It ships 40 regex-based detection rules (ported from an enterprise Warp ADE ruleset), stable per-secret placeholders via sha1 hashing, per-category overrides, an audit log, and a fail-closed mode; PII/financial/healthcare pattern detection is reserved for a paid Enterprise tier.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - CrystalPotato
CrystalPotato is a Crystal-language port of GodPotato, a Windows local privilege escalation tool that abuses the DCOM OXID Resolver and named pipe impersonation to escalate from an account with SeImpersonatePrivilege to SYSTEM. It resolves Windows APIs dynamically, invokes them via indirect syscall stubs, XOR-obfuscates strings at compile time, and can execute commands, spawn reverse shells, or create a local admin account. Compiles to a single dependency-free static binary and was tested on Windows 10, 11, and Server 2025.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - BountySkiller
BountySkiller is a Flask app with two bug-bounty-focused tools: a collector that pulls disclosed HackerOne hacktivity and bug-bounty writeups (plus RSS/Google sources) into local JSON, and "Hunt Buddy," a browser-driven orchestrator that takes a target profile, runs a gap analysis against a set of pluggable bug-class hunting modules (sourced from an external HUNT_TOOLS directory, e.g. SSRF), and produces ranked findings with per-module status and enforced scope.domains restrictions. It exposes a small REST API (/api/hunt/plan, /api/hunt/run, /api/fetch, etc.) for scripting the collection and hunt workflow.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - S1N6H/pentest-harness
pentest-harness is an open-source, plugin-based AI agent framework aimed at authorized penetration tests, bug bounty research, security labs, and CTFs. It provides a "Pentest Mode" offensive-security operating standard, a full agent toolset (shell, filesystem, web research, subagents, background jobs), and a bring-your-own-key multi-provider LLM engine (OpenAI, Anthropic, DeepSeek, Google, Mistral, Groq, OpenRouter, Azure OpenAI) with durable JSONL/SQLite session persistence and an owner-only credential store for API keys.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - IAM Policy Autopilot
IAM Policy Autopilot is an AWS Labs open-source CLI/MCP server that statically analyzes application source code (Python, Go, TypeScript, JavaScript, Java) or a Terraform plan JSON to generate baseline least-privilege IAM identity-based policies, and can also parse AccessDenied error messages to suggest policy fixes. It integrates with AI coding assistants (Kiro, Claude Desktop, etc.) via MCP so assistants can auto-generate scoped IAM permissions instead of overly broad ones, with a --service-hints flag to reduce false-positive permission inclusion.
github.comrepoPublished and added 25 Aug 2026🛡️ Security - Ashmmmm/crockTail
crockTail is a passive OSINT tool that, given a domain, aggregates DNS records, IP/ASN ownership, TLS certificate details, WHOIS data, and crt.sh certificate-transparency history into a single report. It layers analysis on top of the raw data: plain-language warning/info observations (near-expiry or expired certs, recently registered domains, unusual reissuance, historical subdomains from CT logs), multi-resolver (Google vs Cloudflare) DNS cross-verification to flag possible tampering, and a 0-100 confidence score per scan based on module success and cross-check agreement. It supports batch domain queries and query logging, and is explicitly limited to passive lookups and a standard TLS handshake, no port scanning or active probing.
github.comrepoAdded 30 Sep 2026, published 25 Aug 2026🛡️ Security - agentgg
agentgg is an open-source, agentic SAST scanner that uses LLM agents to read source code, follow imports, trace the call graph, and confirm findings before reporting — aiming to reduce the pattern-matching false positives of traditional SAST. It runs locally or as a hosted service, supports full-repo scans or git-diff PR review, and works with multiple model providers (Anthropic, OpenAI, AWS Bedrock, Google Vertex AI, OpenRouter, Ollama); agents are defined as markdown files with YAML frontmatter and are pulled from a community agents catalog.
github.comrepoPublished and added 23 Aug 2026🛡️ Security - Cybermes
Cybermes is an open-source bug bounty and pentest automation framework that pairs a native Go MCP server (cybermes-mcp) with an autonomous Hermes CLI agent, orchestrating recon tools (subfinder, httpx, katana, ffuf, Nuclei, sqlmap), 200+ offensive playbooks covering IDOR/BOLA, JWT, SSRF, XSS, SQLi and cloud misconfig, and a validation-gate workflow that writes non-destructive PoC scripts before compiling findings into Markdown/HTML/PDF reports. It exposes its tools over JSON-RPC 2.0 to AI coding assistants (Claude Desktop, Cursor, Windsurf, Cline, Gemini/Antigravity) so an external LLM can drive scoped, evidence-backed security assessments.
github.comrepoPublished and added 23 Aug 2026🛡️ Security - MinIO Security Lab
A defensive security review lab for MinIO pinned at commit 7aac2a2 (~RELEASE.2025-10-15+11), providing Docker-based single-node, two-node replication, and dual-OIDC environments plus per-finding repro.sh PoCs for issues including service-account key path traversal, server-update SSRF, cross-provider OIDC token acceptance, source-IP/X-Forwarded-For trust, tag-deletion replication bypass, batch job data exfiltration, and secrets exposed via config history. Each of 16+ findings (F-01 through F-16) has ANALYSIS.md with root cause, data-flow trace, and suggested fix, produced via a generate/judge/independent-verify pipeline with cross-vendor adjudication (including an OpenAI/codex-based verifier) and live validation on a lab-built Go binary; ~90 candidates were triaged with ~55 set aside as false positives or intended behavior.
github.comrepoAdded 3 Sep 2026, published 21 Aug 2026🛡️ Security - context-labs/whip
WhipCode (context-labs/whip) is an open-source coding agent written in Go, with a Desktop app, terminal UI and web client on a shared daemon. A recursive language model loop runs short Starlark or JavaScript programs to inspect context, call tools and delegate to subagents. It supports MCP servers, skills and provider-routed models, and solved 20 of 30 tasks in a retained evaluation.
github.comrepoAdded 2 Nov 2026, published 20 Aug 2026🧠 AI - keli-wen/agy-staff
agy-staff is a plugin that lets Claude Code, Codex, Pi and OpenCode delegate work to Google's Antigravity CLI (agy), which runs Gemini 3.8 Flash. It provides five personas (staffer, researcher, reviewer, implementer, ask), a lead orchestration skill and a jobs skill for background tasks. Its Bench v1 compared solo, own-subagent and agy runs on three benchmarks: agy cut Claude Code's host spend by 16% to 50% but raised median task time from 2 to 8 minutes to 13 to 26 minutes.
github.comrepoAdded 20 Oct 2026, published 18 Aug 2026🧠 AI - yetone/cumora
Cumora is a cross-platform team-chat application where AI agents sit alongside humans as first-class participants — holding persistent personas and memory, claiming Kanban work, coordinating with each other, and sending real email — rather than only responding when addressed. Agents can run on Cumora's cloud (per-agent Kubernetes pods driving a multi-hop tool-calling loop over the OpenAI Responses API) or in "Bring Your Own Agent" mode, pairing a local Mac/VPS daemon with an existing coding-agent backend (Claude Code, Codex, Cursor Agent, Gemini CLI, OpenCode, Qwen Code, Google Antigravity, etc.) while keeping provider keys off the server. The repo documents a concrete coordination design — a seen-cursor freshness gate that holds stale replies, atomic claims on units of work, a small-brain triage gate, and a transactional Postgres outbox for realtime fan-out — making it a useful reference for building multi-agent systems that avoid agents colliding on shared work.
github.comrepoAdded 30 Sep 2026, published 17 Aug 2026🧠 AI - vscan
vscan is an open-source, lightweight, cross-platform website vulnerability scanner built for authorized security assessments. It combines port scanning and fingerprint identification (using a merged database of ~6,832 fingerprints from eHole, wappalyzergo, and local rules), login credential brute-forcing, sensitive file detection, and vulnerability PoC checks compatible with both Xray and Nuclei PoC formats. It supports flexible input (STDIN/host/IP/CIDR/URL/TXT) and output formats (JSON/TXT/CSV/STDOUT).
github.comrepoPublished and added 15 Aug 2026🛡️ Security - Andrej Karpathy Skills
A single CLAUDE.md file (also packaged as a Claude Code plugin and Cursor rule) that encodes four principles derived from Andrej Karpathy's public observations on LLM coding failure modes: surfacing assumptions and ambiguity instead of silently guessing, avoiding overengineered/bloated code, touching only what's necessary when editing, and using verifiable success criteria for goal-driven execution loops. It's distributed as a drop-in instructions file, a Claude Code marketplace plugin, and a committed Cursor project rule.
github.comrepoAdded 22 Sep 2026, published 15 Aug 2026🧠 AI - VaultKeepR/vaultkeepr-public
vaultkeepr-public is the MIT-licensed repository behind VaultKeepR, a zero-knowledge password manager. It holds 15 SDK packages published to npm under @vaultkeepr and Solidity contracts on Base L2 that anchor vault locations, recovery fragments and digital legacy, tested with Foundry. Encryption is XChaCha20-Poly1305 with Argon2id (t=3, m=64 MiB, p=4), and docs/THREAT_MODEL.md covers assets, adversaries and trust boundaries. Clients stay in a private repository.
github.comrepoAdded 23 Oct 2026, published 12 Aug 2026🛡️ Security - Cariddi
Cariddi is a Go-based CLI tool that crawls a list of domains/URLs to discover endpoints, secrets, API keys, tokens, and juicy file extensions. It supports proxying through Burp Suite, custom headers, secret/endpoint regex files, JSON/HTML/TXT output, and configurable crawl depth and concurrency, making it a common recon tool in bug bounty and pentest workflows.
github.comrepoAdded 3 Sep 2026, published 12 Aug 2026🛡️ Security - Static Analysis Tools & Linters
analysis-tools.dev's source repository is a community-maintained directory of static analysis tools and linters spanning nearly every programming language, tagged for license (proprietary vs open source), maintenance status, and community endorsement. Beyond general code-quality linters, it catalogs many security-relevant static analyzers such as gosec, flawfinder, OWASP Dependency Check, Mariana Trench, Psalm, PHPStan, govulncheck, and WAP, making it a reference point for discovering SAST tooling per language/ecosystem.
github.comrepoAdded 3 Sep 2026, published 9 Aug 2026🛡️ Security - aurscan
aurscan is a Go-based CLI that hooks into yay/paru to scan a downloaded AUR package's PKGBUILD, .install scriptlets, .SRCINFO and helper scripts before makepkg runs, blocking the build if it looks malicious. It combines offline, quote-aware static rules covering known AUR campaign signatures such as disguised source patch URLs, install-scriptlet worms, masqueraded binary file types, and editor auto-exec triggers with an LLM auditor (Claude Code, Codex, Anthropic API, or a local OpenAI-compatible model) that answers a fixed checklist of yes/no behavioral questions, from which aurscan deterministically derives a verdict, severity and confidence, and fails closed when no backend is available. It documents and defends against real incidents including the July 2025 firefox-patch-bin CHAOS RAT vector, the June 2026 Atomic Arch mass orphan-package takeover pulling a Rust stealer and eBPF rootkit, and the August 2026 xsnow dot-install worm that harvested SSH keys and self-propagated across AUR.
github.comrepoPublished and added 8 Aug 2026🛡️ Security - aoci-spec/aoci-code
AOCI-CODE is a local-first Go CLI and MCP server that keeps a Git-versioned, plain-text index of a codebase and database schema, written by the coding agent itself. Each file gets one FRAS line (function, relations, API, non-obvious constraints) so agents like Codex, Claude Code, Cursor and OpenCode read the system once instead of re-reading the repo. It supports MySQL, PostgreSQL and openGauss, and the current release candidate is v0.1.0-rc23 under FSL-1.1-MIT.
github.comrepoAdded 2 Nov 2026, published 8 Aug 2026🧠 AI - ErSilh0x/VULNaware
Vulnaware is an open-source vulnerability prioritisation engine that ingests Nessus Pro, Greenbone/OpenVAS and MaxPatrol VM exports (CSV or API) plus custom CSV. It enriches findings with CISA KEV, VulnCheck KEV/NVD++, FSTEC BDU and MaxPatrol trending data, then scores them deterministically. Urgent findings go to Telegram, email digests and host-level tickets in Jira Service Management, GLPI, Znuny or osTicket. It runs as Docker containers (Flask dashboard, APScheduler worker, PostgreSQL 17).
github.comrepoAdded 2 Nov 2026, published 6 Aug 2026🛡️ Security - wanmol/goal-flow
goal-flow (goalflow) is a production-oriented framework built on LangGraph that offers two complementary ways to build LLM apps: transpiling Dify Studio's drag-and-drop workflow DSL export into a version-controllable, runnable LangGraph Python file, and building ReAct/Deep/custom agent loops with a vendored agent_kit SDK. It includes a FastAPI HTTP layer, a node library (LLM, code, HTTP, if/else, classifier, iteration, loop, tool, agent, doc-extractor), a chunk-processor that turns raw LangGraph streams into semantic SSE events consumable by pluggable data adapters (Dify/OpenAI/custom), Redis/MySQL persistence, human-in-the-loop interrupts, a skills engine, and Langfuse tracing. It was extracted from an internal production system and reports sustaining 100 concurrent conversations on modest hardware (2 vCPU/4GB per replica).
github.comrepoAdded 30 Sep 2026, published 6 Aug 2026🧠 AI - manyuegong33/r0crawl_skills
r0crawl_skills is a Chinese-language skill library for Codex-style AI coding agents, organized as a router plus 196 specialized modules covering web reverse engineering, Android unpacking, Frida instrumentation, native binary analysis, protocol reconstruction, malware triage, firmware analysis and CTF workflows. Rather than dumping advanced terminology at once, it starts novices with four framing questions (what to analyze, what action matters most, what materials exist, what outcome is wanted) and routes them to deeper workflows via lightweight Python scripts (init_case.py, module_router.py, hash_artifact.py) and ten sanitized example playbooks. It's installed by copying the directory into Codex's skills folder, making it a practical illustration of the "router + many domain modules" pattern for packaging large skill collections for coding agents.
github.comrepoAdded 30 Sep 2026, published 6 Aug 2026🧠 AI - manyuegong33/r0crawl_skills
r0crawl_skills is a beginner-friendly Chinese-language skill library of 196 specialized reverse-engineering modules for Codex-style AI coding agents, with a router that asks scoping questions and directs the agent to the right workflow (web RE, Android unpacking, Frida instrumentation, native binary analysis, protocol reconstruction, malware triage, firmware analysis, CTF). It ships lightweight scripts (case init, module router, artifact hashing) and ten sanitized example playbooks covering DEX dump verification, WebCrypto hooking, native loader tracing, PCAP reconstruction, and selective emulation, plus dedicated modules for CAPTCHA/WAF/anti-bot systems, mini-programs, hybrid apps (Flutter/React Native/Electron), and IDA/Ghidra/Rizin automation.
github.comrepoAdded 30 Sep 2026, published 6 Aug 2026🛡️ Security - CyberSec-Blogs
CyberSec-Blogs is a GitHub-hosted, categorized directory of independent cybersecurity blogs run by practitioners, organized into Red Team (54 entries), Threat Hunting (6), Threat Intelligence, Purple Team, and Detection Engineering sections. The list favors personal blogs publishing original research, tradecraft, and tooling over corporate/vendor content, and is community-maintained via PRs/issues under a CC0 license.
github.comrepoPublished and added 5 Aug 2026🛡️ Security - Precogly
Precogly is an open-source, now-OWASP threat modeling platform (React/TypeScript frontend, Django REST Framework/PostgreSQL backend) offering a collaborative DFD editor with trust zones, TM-BOM import/export, and community library packs linked to MITRE ATT&CK, CAPEC, STRIDE, and LINDDUN. It's positioned as compliance-aware, tracing threats and countermeasures to DORA, the EU Cyber Resilience Act, ASVS, NIST CSF, and SOC 2, and exposes a full OpenAPI REST API meant as scaffolding for AI-driven threat modeling assistants.
github.comrepoAdded 3 Sep 2026, published 5 Aug 2026🛡️ Security - autonomous-ai/openharness
OpenHarness (Autonomous) is an open-source command center for running coding agents such as Claude Code, Codex, Cursor, OpenCode, Devin, Amp and Copilot. A native app and per-machine daemon run each agent in its own tmux pane, with a git worktree per harness. Machines are linked by password, with end-to-end encrypted traffic over direct WebRTC, Cloudflare TURN or a keyless relay. It also supports local models (Ollama, MLX-LM, vLLM, Grid) and a Store of domain-specific harnesses (Blender, CircuitJS, MuJoCo, Godogen, Strudel, RDKit, Typst) defined by a harness.json. An optional open-hardware always-on display device shows agent status.
github.comrepoAdded 16 Oct 2026, published 4 Aug 2026🧠 AI - AMAP-ML/LongHorizon-Harness
LongHorizon-Harness (AMAP-ML, package lh-harness) is a Python tool that wraps existing coding/computer-use agents (Claude Code, Codex, OpenCode, DeepSeek Harness) in a durable plan → act → verify → checkpoint/recover loop. It separates Manager, Executor and Auditor roles, accepts only independently verified progress as task state, and restarts rounds from the original goal plus the last verified checkpoint. It supports GUI and terminal workflows via computer-use MCP plugins (codex-computer-use, open-computer-use, clawdcursor), a React/FastAPI web workbench, per-role model and backend selection, and eval suites including Terminal-Bench 2.1; an arXiv paper accompanies it.
github.comrepoAdded 12 Oct 2026, published 4 Aug 2026🧠 AI - Google Agent Skills
Google's official repository of Agent Skills covering Google products and technologies, including Google Cloud. Skills are installed selectively via `npx skills add google/skills`, and the repo also bundles Google product plugins combining Skills with MCP servers for use in agent harnesses.
github.comrepoAdded 22 Sep 2026, published 3 Aug 2026🧠 AI - openhackai/OpenHack
OpenHack is an open-source, agentic vulnerability scanner CLI that runs a recon -> hunter -> validation -> verification pipeline over a codebase using open-source LLMs. It uses category- and feature-based hunter agents to find candidate vulnerabilities, validator agents to confirm them, and optional Docker-based sandbox plus headless-browser verification to actually exploit findings (e.g. XSS, SQLi, command exec) and confirm them with real HTTP/DOM execution, reporting CVSS-scored findings with fixes.
github.comrepoPublished and added 2 Aug 2026🛡️ Security - QM
QM is an MIT-licensed, self-hosted "multiplayer" agent harness that lets a company deploy a shared coding/ops agent across Slack and a web app, with per-person and per-room isolated sandboxes, memory, keychains, permissions, and crons. Its security model centers on an org-wide posture (Strict pauses every tool call for approval; Auto blocks private-network access and applies optional content screening; Dangerous disables both) layered under a predeclared command policy that hard-denies things like recursive deletes, plus an explicit Isolated/Open sharing posture that governs cross-scope memory and file access with provenance labeling and audit trails. It supports pluggable harnesses (Pi, OpenCode, Codex, Claude Code) behind a common core and documents its threat model and operator assumptions in SECURITY.md.
github.comrepoAdded 3 Sep 2026, published 1 Aug 2026🛡️ Security - ChipWhisperer
ChipWhisperer is NewAE Technology's open-source hardware security toolchain for side-channel power analysis and fault injection research, comprising capture-board hardware/PCB schematics, USB and FPGA firmware, target device firmware examples, and Python APIs (ChipWhisperer Capture and Analyzer) for acquiring and processing power traces. It's widely used to demonstrate and teach attacks like differential power analysis (DPA) and voltage/clock glitching against embedded targets such as microcontrollers and crypto implementations. The repository is undergoing a git-history cleanup for the 6.0 release, splitting files across companion repos including chipwhisperer-jupyter.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Awesome Embedded & IoT Security
A curated GitHub list of embedded and IoT security resources maintained by Fraunhofer FKIE, covering firmware analysis frameworks (FACT, emba, Firmadyne, Binwalk, Ghidra, Radare2), hardware hacking tools (JTAGULATOR, Bus Pirate, ChipWhisperer, Proxmark3, HackRF), RF/wireless gear (RTL-SDR, LimeSDR, UberTooth), books, academic papers on firmware security and fuzzing, real-world case studies of device hacking (D-Link, Huawei, Xerox printers), and CTF challenges (Rhme, Microcorruption, IoTGoat). It serves as a comprehensive entry point for beginners and experts doing embedded/IoT security analysis and hardware pentesting.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Damn Vulnerable DeFi
Damn Vulnerable DeFi is a Foundry-based Solidity smart contract security playground featuring intentionally vulnerable challenges around flashloans, price oracles, governance, NFTs, DEXs, lending pools, smart contract wallets, timelocks, vaults, meta-transactions, and upgradeability. Each challenge presents a prompt and vulnerable contracts; solvers write a Foundry test exploiting the flaw to drain funds or bypass restrictions, making it a benchmark for both human auditors and automated security tooling.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - hackingtool
hackingtool is a console launcher that bundles 215 curated security tools across 21 categories (recon, OSINT, wireless, phishing, forensics, post-exploitation) so users can install and run them without hunting down individual Git repos. Its newer AI layer maps plain-English goals to the right tool and exact command, plans multi-step objectives with confirmation gates, and drafts engagement reports, while emphasizing safe installs (pinned/SHA-256-verified downloads, no curl|bash, list-form subprocess calls, signed releases with SBOM) and refusing out-of-scope asks like DoS or mass-targeting. It also ships a non-interactive orchestrator (`--engagement`/`--pipeline`) that normalizes tool output into findings.json for red team, blue team, OSINT, bug bounty, and DFIR workflows.
github.comrepoAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security - Talaria
Talaria is a single-binary, pure-Go Linux privilege escalation scanner that enumerates misconfigurations (SUID/SGID, sudoers, capabilities, cron, Polkit JS rules, systemd EnvironmentFile overrides) and links them into confirmed multi-stage root-escalation chains using an embedded Dijkstra pathfinder. It runs read-only with no disk writes, executes in milliseconds, detects backport-aware 2026 Linux kernel vulnerabilities (Dirty Frag, Fragnesia, Copy Fail, DirtyClone, CIFSwitch, PinTheft, pedit COW), and exports JSON/SARIF for SIEM and GitHub Code Scanning integration.
github.comrepoAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security - lockfale/OSINT-Framework
OSINT Framework is a curated, categorized index of free (mostly) open-source intelligence tools and resources, organized by data type (username, domain, IP, email, social media, etc.) and rendered as an interactive tree at osintframework.com. Each entry in the underlying arf.json is tagged with metadata like whether it requires local install (T), a Google dork (D), registration (R), or manual URL editing (M), plus richer fields such as input/output type, pricing, and opsec notes. It's a long-standing community reference for recon and investigation tradecraft across infosec and other fields.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - awesome-osint-arsenal
An awesome-list repo that claims 753+ OSINT and security tools across 50 categories. Sections cover username, email, phone, domain/IP, geolocation, image, breach-search, dark web, web scanning and password-cracking tools, plus red team, blue team, DFIR, hardware and training sections. It ships multi-distro installer scripts (install.sh, osint.sh, redteam.sh, blueteam.sh, forensics.sh, hardware.sh, labs.sh, termux.sh) for Kali, Debian and Ubuntu, with partial Arch/Fedora support and a Termux subset. It also gives short usage walkthroughs such as a subfinder + amass + httpx recon chain. Some entries are dual-use (people search, face recognition, phone exploitation, IP camera dorking), and the README says the repo is for authorized research only.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Web3 Security Tools Hub
A curated GitHub repo cataloging AI tools for smart-contract security auditing, split into free/open-source and paid/closed-source categories and organized by chain/language: Solidity/EVM, Rust/Solana, Move/Sui, ZK/Circom, and multi-language tools. Maintained by pashov, it's meant as a directory for finding AI-assisted auditing tooling rather than a single tool itself.
github.comrepoAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security - glsec
glsec is a security linter for GitLab CI (.gitlab-ci.yml) configuration files, analogous to zizmor/actionlint for GitHub Actions. It detects misconfigurations like mutable image tags, unquoted user-controlled CI variables in scripts, and other issues mapped to 84 rules across 8 OWASP CI/CD Security categories (excluding IAM and logging, which require platform-level access). It supports baseline/ignore workflows, ShellCheck integration, SARIF/Code Climate/JUnit output for GitLab dashboards, a pre-commit hook, and a Claude Code plugin, and ships releases with Sigstore/cosign signing and SLSA provenance attestations.
github.comrepoPublished and added 29 Jul 2026🛡️ Security - Recon-Skills
Recon-Skills is a curated collection of SKILL.md playbooks for external web security assessments, organized into auth (SSO/OAuth/SAML/MFA), chains (multi-step attack-path analysis), infra, recon (subdomain/DNS/port/tech discovery, route/parameter/API mapping), and redteam (vulnerability-class and platform-specific validation) categories. Each skill documents prerequisites, procedure, pitfalls, and verification criteria, and the skills are designed to be followed manually or loaded as task context by an automation system for authorized penetration testing engagements. It includes a validator script (validate_skills.py) and style/contribution guides to maintain a consistent quality baseline across skills.
github.comrepoPublished and added 29 Jul 2026🛡️ Security - YuroGod/VMPStaticUnpacker
VMPStaticUnpacker is a Python tool that statically unpacks VMProtect-protected Windows PE binaries without executing them, supporting both the legacy plaintext PACKER_INFO metadata format and the compact rotating-XOR format seen in VMProtect 3.9.5 PE32+ samples. It recovers the destination key by XORing the encoded destination with the first packed section's RVA and rolling the key with ROL32(key,7), then validates candidate tables and LZMA streams before rebuilding a memory-image PE for static analysis. It does not devirtualize protected code, recover the original entry point, strip the VMProtect runtime, or fix imports.
github.comrepoAdded 2 Oct 2026, published 29 Jul 2026🛡️ Security - Dalfox
Dalfox is an open-source XSS scanning and parameter analysis tool, rewritten in Rust for v3 (previously Go, preserved on the v2 branch). It automates discovery via parameter mining and static/BAV analysis, detects reflected, stored, and DOM-based XSS with DOM/AST verification, and includes WAF fingerprinting with confidence scoring and bypass tracking, plus a REST API and MCP stdio server for extensibility.
github.comrepoPublished and added 25 Jul 2026🛡️ Security - ShortDot Zone Abuse Evidence
PhishDestroy's shortdot-evidence is a daily-updated GitHub investigation into ShortDot SA, the Luxembourg registry operator behind the .icu, .bond, .cyou, .sbs, .cfd, .buzz and .qpon gTLDs, documenting that 51,985+ tracked domains impersonate brands like Chase, Binance, MetaMask and Ledger and that ~70% of registered domains in these zones carry no DNS records (metric-padding rather than legitimate use). It publishes machine-generated IOC/blocklist files and analytics built from a per-TLD zone-file pull cross-referenced against Spamhaus DBL, SURBL, OpenPhish, URLhaus, PhishTank and AlienVault OTX, and ties the zones to concrete criminal cases (FBI's LabHost domain list, Google v. DOES/Yucheng Chang RICO suits, the Revolver Rabbit XLoader/Formbook C2 campaign using 500k+ .bond domains). It also details structural conflicts of interest between ShortDot, its registry infrastructure provider Team Internet Group/CentralNic, registrar partner NameSilo, and the brand-protection vendor NameBlock, backed by Interisle Consulting Group phishing-volume statistics.
github.comrepoPublished and added 25 Jul 2026🛡️ Security - Birfy/agentdescent
agentdescent is a Python framework that treats self-improving agents as an optimization problem: N workers propose diffs (edits) to a shared skill/prompt/harness artifact in parallel, and a barrier-free aggregator merges them via conflict resolution, fusion and statistical acceptance rather than gradient averaging, committing winners to a version-controlled ledger. It ships a single `evolve()` entry point with pluggable strategy, scorer, and proposal functions, an MCP server and CLI for agent-triggered runs, and faithful reimplementations of 20 published self-evolution algorithms (ACE, GEPA, EvoSkill, SkillOpt, ADAS, DGM, OpenEvolve, ERA, PromptBreeder, AFlow, Self-Refine, Reflexion, SICA, Gödel Agent, Voyager, SkillWeaver, Absolute Zero, R-Zero, Agent0, Genesis) that plug into the same engine for apples-to-apples comparison. The accompanying paper (Chen, 2026) gives a closed-form condition for when concurrent edits can merge and reports confidence intervals rather than false-precision p-values.
github.comrepoAdded 30 Sep 2026, published 24 Jul 2026🧠 AI - aniqfakhrul/CVE-2026-54121
Certighost is a Python PoC for CVE-2026-54121, an Active Directory Certificate Services attack that spins up rogue SMB/LSA and LDAP listeners to intercept the CA's NetLogon-based identity resolution during certificate enrollment. By impersonating a low-privileged computer account and redirecting the CA's lookups to the target Domain Controller's identity, the tool causes the CA to issue a valid certificate for the DC, then uses PKINIT with that certificate to retrieve the DC's Kerberos TGT/ccache and NT hash — a full domain-compromise chain from a single low-privileged account. The repo includes fixes for an in-the-wild NetLogon trust-account error (STATUS_NOLOGON_SERVER_TRUST_ACCOUNT) and a SAN-spoofing bypass for CAs enforcing ESC6-style EDITF_ATTRIBUTESUBJECTALTNAME2 protections.
github.comrepoAdded 5 Oct 2026, published 23 Jul 2026🛡️ Security - gowitness
gowitness is a Golang website screenshot utility that drives Chrome Headless to capture screenshots of web interfaces at scale from the command line, ingesting targets from URL lists, CIDRs, Nmap, or Nessus results. It can also capture request/console logs, headers, and cookies, writing results to SQLite, JSONL, or CSV, with a bundled web-based report viewer and API for triaging large recon datasets.
github.comrepoAdded 3 Sep 2026, published 23 Jul 2026🛡️ Security - SeClaw
SeClaw is a benchmark framework for evaluating security risks of autonomous LLM agents, combining spec-driven synthesis of security tasks (covering resource, task, environment, and intrinsic-agent risk categories) with execution-based evaluation in a Docker sandbox. The repo ships SeClaw-Bench, a public dataset of 150 OpenClaw task directories, plus batch-execution scripts that record full agent trajectories (tool calls, file ops, outputs) and grade them against a multi-dimensional risk rubric covering information leakage, privilege misuse, content safety, and compliance risks, rather than only judging final responses.
github.comrepoPublished and added 22 Jul 2026🛡️ Security - capitalone/VulnHunter
VulnHunter is Capital One's open-source agentic AI vulnerability scanner built as a set of Claude Code skills (/vulnhunt, /vulnhunter-fix, /vulnhunt-fix-verify) that runs on Claude Opus. Instead of pattern-matching like traditional SAST, it does attacker-first forward analysis from entry points, runs a "falsification engine" to discard unexploitable findings, and generates evidence-backed remediation patches; it also ships a headless agent runtime and a benchmarking harness tested against OWASP NodeGoat, Juice Shop, and WebGoat.
github.comrepoAdded 19 Jul 2026🛡️ Security - Argo
Argo is an LLM-native static application security testing tool that drives Claude Code, Codex, Gemini, or local models (via Ollama/LM Studio) as an AI analyst to audit source code, extract security invariants, and produce reviewable vulnerability reports with optional patch generation and ASan-verified proof-of-concept crashes. It positions itself as a complement to rule-based SAST tools like CodeQL and Semgrep, targeting logic/authorization bugs that fixed patterns miss, and has been used to find real, disclosed vulnerabilities across 15 audited open-source projects (53 PRs, 2 CVEs). It supports two modes — general code audit and bug-bounty triage with scope-enforced, read-only, opt-in live verification guardrails.
github.comrepoAdded 3 Sep 2026, published 18 Jul 2026🛡️ Security - luqman-v1/9router-go
9router-go is a single-binary Go port of 9Router, an LLM gateway that sits between CLI coding tools (Claude Code, Cursor, Codex, Cline, OpenClaw, Gemini CLI, OpenCode) and 40+ AI providers/100+ models. It adds RTK token compression (claimed 20-40% token savings on tool_result content), tiered auto-fallback (subscription → cheap → free providers), multi-account round-robin, per-key proxy pools, and an embedded Svelte dashboard backed by SQLite, with database compatibility to share state with the original Next.js 9Router. It targets the practical problem of coding-agent subscription quota exhaustion and token cost, not a research contribution.
github.comrepoAdded 7 Oct 2026, published 18 Jul 2026🧠 AI - CyberSunil/LLMVault
LLMVault is a self-hosted, deliberately-vulnerable training range modeled on WebGoat but for LLM applications, covering 25 labs across the OWASP Top 10 for LLM Applications (2025) - prompt injection, jailbreaking, data/model poisoning, agent exploitation, model extraction, and insecure downstream output handling. It ships two modes: a scored Play Mode with scripted assistants for repeatable flag capture, and an unscripted Live Mode that points the same attacks at a real local Ollama model (qwen2.5:3b-instruct) with a freshly minted per-session secret, requiring the player to actually talk the model into leaking it. Each lab pairs the attack with a written defense explanation, and an expert tier is shipped AES/Fernet-encrypted and unlocked manually by the maintainer.
github.comrepoPublished and added 18 Jul 2026🛡️ Security - VulnHunter (Capital One)
VulnHunter is Capital One's open-source agentic AI security scanner, implemented as a set of Claude Code skills (/vulnhunt, /vulnhunter-fix, /vulnhunt-fix-verify) that require Claude Opus. Instead of traditional sink-first SAST pattern matching, it reasons forward from attacker-accessible entry points (APIs, uploads, network messages), runs a 'falsification engine' to discard unexploitable findings, and generates evidence-backed exploit paths and targeted code fixes; it also ships a headless agent for CI/CD-scale scanning and a benchmarking harness against corpora like Juice Shop, WebGoat and NodeGoat.
github.comrepoAdded 22 Sep 2026, published 18 Jul 2026🛡️ Security - GoogleCloudPlatform/k8s-aibom
k8s-aibom is a Kubernetes controller from GoogleCloudPlatform that generates CycloneDX 1.6 ML-BOM documents at runtime for AI workloads — inference services (vLLM, TGI, Triton, Ollama), agent stacks (LangChain, AutoGen, CrewAI), RAG/vector DB infrastructure (Milvus, Qdrant, Weaviate), and training/eval jobs — by watching Kubernetes API objects with no privileged access. Each BOM attribute carries a declared/inferred/unresolved confidence flag and evidence locator, and the project positions its output as auditor-traceable evidence for EU AI Act Article 12/50, NIST AI RMF, and ISO/IEC 42001 compliance, with redaction filters, immutable GCS write-once sinks, and Sigstore-signed release attestations.
github.comrepoPublished and added 18 Jul 2026🛡️ Security - AI-Powered Threat Modeling
AITM is an open-source Python CLI (MIT licensed) that automates STRIDE threat modeling of system architectures using LLMs via Bedrock, OpenAI, or local Ollama. Given a text description or architecture diagram image, it identifies assets and data flows, generates STRIDE-categorized threats with CWE mapping (e.g. CWE-89 for SQLi), scores risk on a 5-level matrix, and outputs actionable mitigations in Markdown or JSON. The engine is stateless with a Pydantic data contract, designed to later support a REST API and frontend; an enterprise edition with additional features is offered commercially.
github.comrepoAdded 3 Sep 2026, published 17 Jul 2026🛡️ Security - Destructive Command Guard (dcg)
Destructive Command Guard (dcg) is a Rust-based hook that intercepts and blocks catastrophic commands (git reset --hard, rm -rf, DROP TABLE, kubectl delete namespace, terraform destroy, etc.) before AI coding agents like Claude Code, Codex CLI, Gemini CLI, GitHub Copilot CLI, and Cursor can execute them. It uses a modular "pack" system covering 50+ categories (databases, cloud providers, Kubernetes, secrets managers, CI/CD, storage, DNS, payments) plus a three-tier heredoc/inline-script AST scanning pipeline to catch destructive commands hidden inside python -c/bash -c payloads, and a dedicated "careful_company_running_windows" preset that also blocks data-exfiltration channels (webhooks, uploads, tunnels) and attempts to disable security controls. Configurable via TOML with agent-specific trust profiles, allowlists, and fail-closed/fail-open policies for unattended agent sessions.
github.comrepoPublished and added 15 Jul 2026🛡️ Security - Mantis
Mantis is Google's open-source suite of AI agent skills plus an ADK-based reference harness for autonomous security code review. It walks a codebase to build a semantic index and threat model, generates and executes vulnerability research hypotheses across agents, deduplicates and triages findings to combat LLM hallucination, attempts reproduction (static guesses up to spun-up mock servers), chains findings for impact, and patches issues in an adversarial verify-the-fix loop, calibrating severity against a rubric to avoid inflated "critical" spam. It explicitly warns it is demonstration-only, non-deterministic, and requires isolated sandboxing plus human expert verification before any findings are reported.
github.comrepoPublished and added 15 Jul 2026🛡️ Security - Giskard-AI/giskard-oss
Giskard is an open-source Python testing/evaluation library for agentic and LLM systems, rewritten in v3 as a modular set of packages (giskard-checks, giskard-scan, giskard-core, giskard-llm, giskard-agents). giskard-scan is the red-teaming layer: it auto-generates adversarial test suites from a plain-language agent description, covering prompt injection, harmful content, stereotypes, and misinformation across OWASP LLM Top-10 categories, and includes a built-in prompt-injection payload dataset. giskard-checks provides LLM-as-judge and assertion-based evals (Groundedness, Conformity) for catching regressions and enforcing safety rules in multi-turn agent conversations; the legacy v2 also offered a tabular ML bias/robustness scanner and RAGET for RAG test-set generation.
github.comrepoPublished and added 14 Jul 2026🛡️ Security - magnus919/agent-skills
A sprawling open-source collection of 100+ reusable "Agent Skills" (markdown instruction packs with YAML frontmatter following the open Agent Skills format) for agentic systems, compatible with Claude Code and any framework that supports the standard. Skills span multi-agent orchestration frameworks (AutoGen, CrewAI, LangChain, LangGraph, LlamaIndex, DSPy, Haystack, a PydanticAI-based multi-agent debate tool), production agent operations, evals, and AI governance, alongside dozens of narrower domain skills — CLI integrations for Jira, Confluence, Notion, Linear, HubSpot, Ghost, Fireflies, Grafana, PostgreSQL, Kubernetes, Docker Compose, FFmpeg, Ghidra-based binary triage, FPGA/ESP32 hardware design, and more. The page text was truncated at 40,000 of 71,286 characters, so later entries in the catalog are not reflected here.
github.comrepoAdded 1 Oct 2026, published 11 Jul 2026🧠 AI - DataDog/guarddog
GuardDog is DataDog's CLI tool that scans PyPI, npm, Go modules, Rust crates, RubyGems, GitHub Actions, and VSCode extensions for malicious packages using YARA-based static analysis and registry metadata detectors. It correlates code capabilities with threat indicators (mapped to MITRE ATT&CK stages) to produce a 0-10 risk score, aiming to reduce alert fatigue compared to traditional SAST tools, and runs archive extraction and source analysis inside a kernel-level sandbox (Landlock/Seatbelt via nono) to mitigate path-traversal/code-execution vulnerabilities such as CVE-2022-23530, CVE-2022-23531, CVE-2026-22870, and CVE-2026-22871.
github.comrepoPublished and added 11 Jul 2026🛡️ Security - SyscallX-18113/Apkx-Hunter
APKX-Hunter is an open-source Android static analysis framework written in C, built for reverse engineering, malware analysis, OWASP MASVS compliance scanning, and bug bounty/pentesting work. It decompiles APK/APKM/APKS/XAPK/ZIP packages via JADX or APKTool, extracts hardcoded secrets, endpoints, permissions, exported components, and native libraries, and scores detected secrets with a lightweight offline C-based ML classifier (166 MASVS detection patterns across 15 categories). It was showcased at Black Hat Europe Arsenal and tested against the OWASP UnCrackable Level 4 app.
github.comrepoAdded 30 Sep 2026, published 11 Jul 2026🛡️ Security - loop-js/loop.js
loop.js is a TypeScript framework for "loop engineering": you define a goal and a verification bar, and the engine runs an agent through repeated Rounds (Execute → Handoff → Verify → Persist) with fresh context each round, memory read back from disk, until a separate skeptical judge agent rules the goal met, gives up, or a budget guard (rounds/usd/timeout) fires. It ships a CLI (`loop run`, `loop status`, `loop cron`) for one-off runs or scheduled/recurring loops (local or deployed to Modal), a typed async-iterable event stream for embedding in products, and runs its worker/judge agents on the Claude Agent SDK. It's positioned against bare `while(true)` agent loops and Claude Code's own `/loop` command, aiming at loops that outlive a terminal session — cron-triggered chores, financial-trade auditing, or long-running builds — where "done" must be judged by an agent the worker can't influence.
github.comrepoAdded 30 Sep 2026, published 10 Jul 2026🧠 AI - DataDog/pathfinding-labs
Pathfinding Labs is DataDog's open-source platform (Go CLI 'plabs' + Terraform modules) for deploying intentionally vulnerable AWS resources into sandbox accounts to practice attacking and detecting IAM privilege-escalation paths. It ships modular labs across five categories — self-escalation, one-hop/multi-hop principal traversal, CSPM misconfigurations, toxic combos, and cross-account (dev/ops-to-prod) chains — each with demo/cleanup scripts, expected CSPM alerts, and MITRE ATT&CK mappings (e.g. T1098.001). It's positioned as a successor/companion to projects like IAM Vulnerable and Stratus Red Team for hands-on cloud identity attack training.
github.comrepoPublished and added 4 Jul 2026🛡️ Security - microsoft/RAMPART
RAMPART (Risk Assessment & Measurement Platform for Agentic Red Teaming) is a Microsoft-built pytest-native framework for writing and running safety and security tests against agentic AI applications. It structures tests around adversarial attacks, benign failure modes, and harm categories, using evaluation-driven assertions integrated directly into pytest workflows.
github.comrepoPublished and added 4 Jul 2026🛡️ Security - Tencent/AI-Infra-Guard
AI-Infra-Guard (A.I.G) is Tencent Zhuque Lab's open-source AI red-teaming platform that fingerprints running AI services (e.g. vLLM, LangFlow, MLflow, llama.cpp) against a library of 2000+ CVE rules, scans MCP servers and Agent Skills for vulnerabilities using the SkillTrustBench T01–T09 taxonomy, and runs multi-turn jailbreak evaluations (Many-Shot, PAIR, GOAT, ActorAttack). It also ships an LLM API poisoning/model-substitution detector, a plugin framework for community-contributed fingerprint/vuln/MCP rules, and accompanying research (FORGE-Bench, RogueHandoff-20, SkillJack) on agent loss-of-control and skill backdoors.
github.comrepoAdded 2 Jul 2026🛡️ Security - Kogaro
Kogaro is a Go-based Kubernetes cluster-hygiene validator that continuously scans clusters (and can run one-off against manifests in CI/CD) for silent configuration failures: dangling references to missing ConfigMaps/Secrets/ServiceAccounts/IngressClasses, insecure pod/container SecurityContexts (root user, privileged mode, missing capabilities drops), missing resource requests/limits, container image/architecture mismatches, and NetworkPolicy coverage gaps. Each finding gets a structured KOGARO-CCC-XXX error code for automated alerting/ticketing, and it exposes Prometheus metrics with leader-election/HA support for production deployment via Helm.
github.comrepoAdded 3 Sep 2026, published 25 Jun 2026🛡️ Security - SkillSpector
SkillSpector is NVIDIA's open-source scanner for AI agent skills (used by Claude Code, Codex CLI, Gemini CLI, etc.), detecting 71 vulnerability patterns across 17 categories including prompt injection, data exfiltration, privilege escalation, MCP tool poisoning, and supply-chain issues via static analysis, AST checks, YARA rules, and optional LLM semantic evaluation. It cites research showing 26.1% of a 31,132-skill sample contain vulnerabilities and 5.2% show likely malicious intent, and can run as a CLI, MCP server, or install gate producing JSON/SARIF risk scores and DO_NOT_INSTALL/CAUTION/SAFE recommendations.
github.comrepoPublished and added 14 Jun 2026🛡️ Security - open-source-web-scanners
A GitHub list curated by psiinon (creator of OWASP ZAP) cataloging open-source web security scanners, ranked by GitHub/GitLab stars. Tools are grouped by category: general unknown-vulnerability scanners, known-vulnerability scanners, fuzzers, CMS-specific scanners, API scanners, and tools focused on specific vulnerability classes.
github.comrepoAdded 3 Sep 2026, published 10 Jun 2026🛡️ Security - OWASP Noir
OWASP Noir is a static analysis (SAST) tool that reads source code to extract every endpoint an application exposes — paths, methods, parameters, headers, cookies, and their originating files — across 205 supported frameworks, with an LLM fallback (OpenAI/Ollama) for unsupported ones. The endpoint inventory (including shadow APIs and undocumented routes) is exported as JSON/YAML/OpenAPI/SARIF/cURL/Postman/HTML to feed DAST scanners (ZAP, Burp Suite, Caido, Gori), human security reviewers, and AI SAST auditors, with optional --ai-context enrichment (guards, sinks, validators, callees) and GitHub Action/CI integration.
github.comrepoPublished and added 24 May 2026🛡️ Security - PentAGI
PentAGI is an open-source, self-hosted autonomous AI agent system built in Go with a React/GraphQL frontend that orchestrates multiple LLM-driven agents to perform complex penetration testing tasks end-to-end. It integrates with LLM providers like OpenAI and Anthropic and packages common offensive security tooling so an agent can plan, execute, and iterate on pentest workflows with minimal human intervention.
github.comrepoAdded 3 Sep 2026, published 23 May 2026🛡️ Security - We5ter/Scanners-Box
Scanners-Box is a curated GitHub collection aggregating open-source security scanners self-developed by security practitioners, organized by category (web, host, port, weak-password, subdomain, SSRF, and more). It serves as a reference index for finding vulnerability scanners and reconnaissance tools built and shared by the security community.
github.comrepoPublished and added 23 May 2026🛡️ Security - musana/CF-Hero
CF-Hero is a Go-based recon tool that uncovers the real origin IP of Cloudflare-protected web applications by correlating current/historical DNS records (A, TXT/SPF), OSINT search engines (Shodan, Censys, ZoomEye), SecurityTrails historical DNS, and sub/related-domain host-header comparison. It validates candidate IPs by connecting directly over HTTP(S) and comparing HTML titles against the target, and supports custom JA3 fingerprints, proxies, and concurrent scanning to reduce false positives.
github.comrepoPublished and added 21 May 2026🛡️ Security - Open ASM Platform
Open ASM (OASM) is an open-source, self-hostable Attack Surface Management platform that continuously discovers internet-facing assets (IPs, ports, services, technologies), runs distributed vulnerability/misconfiguration scans via pluggable connector containers wrapping tools like nuclei, subfinder, httpx, naabu, and dnsx, and exposes an MCP server so AI assistants (OpenAI, Anthropic, Google models) can query and analyze the collected asset inventory in natural language. Scanning capability is decoupled into a companion oasm-connectors repo whose manifest lets Core API resolve and dispatch versioned Docker connector images to auto-scaling workers without requiring a platform release.
github.comrepoAdded 3 Sep 2026, published 17 May 2026🛡️ Security - FoxGuard
FoxGuard is a fast local/CI security scanner offering 200+ built-in rules across 12 languages, cross-file taint tracking for 14 languages, secrets scanning, OSV-backed dependency (SCA) scanning, and a post-quantum crypto (PQC) audit that flags quantum-vulnerable primitives (RSA, ECDSA/DSA, ECDH/DH) against CNSA 2.0 deadlines while also inventorying already-adopted PQC algorithms (ML-KEM, ML-DSA, SLH-DSA, FN-DSA, HQC). It ships a Semgrep/OpenGrep-compatible YAML rule bridge covering ~98% of the public Semgrep registry, outputs to SARIF/CycloneDX 1.6 CBOM/Semgrep-JSON, and integrates via GitHub Action, pre-commit, VS Code, Claude Code plugin, and MCP server, plus an interactive TUI for reviewing findings and baselines. It's part of the "0sec" open cybersecurity harness project.
github.comrepoAdded 3 Sep 2026, published 16 May 2026🛡️ Security - AG Kit
AG Kit is an open-source Antigravity-first agent engineering toolkit that installs a `.agents/` workspace contract of rules, skills, specialist agents, workflows, persistent memory, and MCP configuration for Google's Antigravity coding-agent runtime. It ships a native PreToolUse safety hook that blocks destructive commands (root-filesystem deletion, drive formatting, raw-disk overwrites) without replacing Antigravity's own permissions or sandboxing, plus a CLI (`ag-kit init`/`update`/`rollback`) with merge-aware, backed-up updates and SemVer-versioned, drift-checked toolkit manifests.
github.comrepoAdded 22 Sep 2026, published 15 May 2026🧠 AI - OWASP/DockSec
DockSec is an OWASP Lab Project CLI that wraps Trivy, Hadolint, and Docker Scout to scan Dockerfiles, images, and Compose files, then uses an AI provider (OpenAI, Anthropic, Google, or local Ollama) to correlate findings, cut noise, and generate plain-English remediation suggestions. It supports CI/CD gating via exit codes, baselines, and auditable waiver files, outputs SARIF/CycloneDX SBOM/HTML/PDF/JSON/CSV/Markdown reports, and redacts secrets before any content reaches an LLM, with a fully offline/local-only mode for air-gapped teams.
github.comrepoPublished and added 14 May 2026🛡️ Security - GenAI App Security Checklist
A 258-item, 17-category security checklist targeting vulnerabilities that AI coding assistants (Claude, GPT, Gemini, Grok, Mistral, Copilot) commonly introduce, each item tagged with severity and a static/runtime/config detection method. Includes a companion prompt.md that turns the checklist into an automated scan runnable via Claude Code, Gemini CLI, or OpenAI Codex CLI against a local codebase, covering issues like prompt injection via user-supplied system prompts, missing auth middleware, hardcoded secrets, exposed API keys in frontend env vars, LLM-based auth decisions, unsandboxed agentic shell/filesystem access, and vector DB tenant isolation gaps.
github.comrepoAdded 3 Sep 2026, published 13 May 2026🛡️ Security - IDP Zero-Dollar
A companion GitOps playbook/repo for building a free, self-hosted "AWS-equivalent" Kubernetes platform from three bare-metal Linux boxes using k3s, Cilium, cert-manager, Traefik, Argo CD, Forgejo, Vault, Keycloak, kube-prometheus-stack, Loki, Kyverno, and Velero. It walks through the full security-relevant stack end to end: OS hardening (SSH lockdown, ufw, fail2ban), Cilium NetworkPolicy as CNI, Let's Encrypt DNS01 wildcard certs, Vault as the source of truth for secrets synced via External Secrets Operator (never committing secrets to Git), Keycloak OIDC for centralized identity across Argo/Grafana/Forgejo/Vault, Kyverno pod-security policies in audit-then-enforce mode, and Velero + Vault Raft snapshot backup/DR with quarterly restore drills. It closes with a candid list of what self-hosting gives up versus managed cloud (CVE patch cadence, DDoS exposure, compliance evidence, etcd/HA operational risk).
github.comrepoAdded 3 Sep 2026, published 13 May 2026🛡️ Security - Hack Skills
hack-skills is a GitHub repo (yaklang/hack-skills) that packages offensive security knowledge into installable "Agent Skills" — one master entry, six category entries, and 102 deep-topic SKILL.md files across 14 domains including web/API security, auth, Linux/Windows/macOS privilege escalation, Active Directory attacks, mobile, binary exploitation, reverse engineering, crypto attacks, blockchain/smart contracts, AI/LLM security, network pivoting, and forensics. It's designed for AI coding agents (installed via `npx skills add yaklang/hack-skills` or a raw SKILL.md URL) to use during authorized pentesting, bug bounty, and CTF work, and explicitly strips destructive PoCs (DROP/TRUNCATE, FLUSHALL, service shutdown/DoS) in favor of non-destructive proofs like time-based SQLi and read-only recon, while retaining RCE/webshell/reverse-shell primitives as access proofs.
github.comrepoAdded 3 Sep 2026, published 13 May 2026🛡️ Security - GigaChad GRC
GigaChad GRC is a self-hosted, containerized Governance, Risk, and Compliance platform covering controls/evidence, framework assessments, policy lifecycle, third-party risk management (TPRM), a trust center, and audit management. It's built as Node.js/NestJS microservices behind a Traefik gateway with PostgreSQL, Redis, Keycloak SSO, and RustFS storage, deployable via a one-command Docker Compose script, and licensed under Elastic License 2.0.
github.comrepoAdded 3 Sep 2026, published 13 May 2026🛡️ Security - knostic/OpenAnt
OpenAnt is Knostic's open-source Apache 2 licensed LLM-based vulnerability discovery tool that runs source code through a two-stage pipeline, an agentic detection phase followed by an attack and verification phase, to filter out false positives and surface exploit-verified findings. It is a Go CLI with a Python analysis backend supporting Go, Python, and several beta languages including JavaScript, C, PHP, Ruby, Zig, Swift, and Rust, with pluggable LLM providers such as Anthropic, OpenAI, Google, Ollama, OpenRouter, and Bedrock, plus diff and PR scoped scanning for CI and a local web UI.
github.comrepoPublished and added 12 May 2026🛡️ Security - Titus by Praetorian
Titus is Praetorian's open-source secrets scanner that detects credentials, API keys, and tokens across source code, git history, container images, and binary files using 487 detection rules drawn from NoseyParker and Kingfisher. It combines Hyperscan/Vectorscan-accelerated regex matching with live credential validation (checking secrets against AWS/GitHub/etc APIs) and risk-based severity scoring, and ships as a CLI, Go library, Burp Suite extension, and Chrome extension sharing one detection engine.
github.comrepoPublished and added 10 May 2026🛡️ Security - Mirage
Mirage is an open-source virtual terminal and filesystem for AI agents that mounts services like S3, Slack, Redis and Gmail under one POSIX-like root and virtualizes CLIs and runtimes. It provides agent-focused security controls: allow/ask/deny profiles for commands, hide/show rules for files, a scriptable policy engine that gates every filesystem operation and session write, and credential resolution via AWS Secrets Manager, 1Password and Auth0. The goal is fine-grained control over what an AI agent can execute and see, reducing the blast radius of agent tool use.
github.comrepoAdded 3 Sep 2026, published 8 May 2026🛡️ Security - SanMuzZzZz/LuaN1aoAgent
LuaN1aoAgent v2 is a TypeScript rewrite of an autonomous, authorized security-research agent built on the Pi SDK, splitting work into Planner, Executor, and Observer (Supervisor/Projector) roles that coordinate via a persisted task graph and an evidence-backed reasoning/operation graph. It runs Executors in per-task Docker sandboxes with a protocol-aware Go network Gateway that enforces IP/domain scope, supports CVE/advisory lookups via NVD and web search, browser rendering, and traffic capture/replay through an authenticated web workbench. The project targets authorized pentesting/CTF-style engagements, with explicit scope enforcement, SOCKS5 egress routing, and human-facing observability (TUI + web UI) for tracing hypotheses to confirmed vulnerabilities and exploits.
github.comrepoPublished and added 8 May 2026🛡️ Security - DefenseClaw
DefenseClaw is a Cisco AI Defense open-source project providing security governance for OpenClaw and other agentic AI runtimes. It combines a Python operator CLI, a Go gateway, connector hooks, policy engine, capability scanners, and observability exporters to scan agent capabilities before use, inspect runtime traffic, and export durable audit evidence — positioned explicitly as an enforcement/evidence layer, not a guarantee of risk-free agent behavior.
github.comrepoAdded 3 Sep 2026, published 7 May 2026🛡️ Security - DeepTeam
DeepTeam is an open-source, locally-runnable red teaming framework for LLM applications, agents, and RAG pipelines, built on the DeepEval evaluation library. It simulates jailbreaking, prompt injection, and multi-turn adversarial attacks against 50+ vulnerability categories such as PII leakage, BOLA, BFLA, SQL injection, SSRF, and agentic goal theft, maps results to OWASP, NIST, MITRE, BeaverTails, and Aegis frameworks, and ships production guardrails to block the same issues at runtime.
github.comrepoPublished and added 7 May 2026🛡️ Security - 0xhackerfren/ProcMon-MCP
ProcMon-MCP is an MCP server that gives AI assistants like Claude direct access to Windows internals: live process enumeration, ETW kernel trace start/stop via logman/tracerpt, static PE import/export analysis with API category tagging, Security event log queries (audit IDs 4688/4624/4672/4648), and service/driver/minifilter enumeration. It's positioned as a POC for security researchers and reverse engineers who want an LLM that can query kernel traces, driver lists, and process memory instead of alt-tabbing to Task Manager or Process Monitor. Several tools (ETW tracing, Security log reads) require administrator privileges and can trigger UAC prompts.
github.comrepoPublished and added 7 May 2026🛡️ Security - DragonJAR/Android-Pentesting-Skill
Android-Pentesting-Skill is an open-source "skill" package that turns an AI coding agent (Claude Code, OpenCode, etc.) into an Android APK security auditor. It orchestrates APKTool/JADX decompilation, MASTG-aligned Semgrep static rules, source-to-sink tracing, a Runtime Defense Analysis engine that maps detected RASP/anti-tampering protections (root detection, SSL pinning, Frida detection, SafetyNet, Approov, DexGuard, etc.) to reusable Frida bypass profiles, and CVSS 4.0/MASVS-scored professional reporting, plus smali patching/repackaging workflows for authorized lab use. It ships 37+ bundled Frida scripts, 70+ Semgrep MASTG rules, and framework-specific handling for Flutter, React Native, Cordova, and Unity apps.
github.comrepoPublished and added 7 May 2026🛡️ Security - IronCurtain: Secure AI Agent Runtime
IronCurtain is a research-prototype runtime that constrains autonomous AI agents (Claude Code, Goose, or its own builtin agent) by compiling a human-written "constitution" into deterministic policy rules enforced on every MCP tool call. It treats the LLM as untrusted, mediating all filesystem/git/network/API access through a policy engine (allow/deny/escalate), a V8 isolate sandbox for its builtin agent, and a network-isolated Docker mode with a TLS-terminating MITM proxy for external agent tools. It also ships multi-agent workflow orchestration (e.g., a vulnerability-discovery pipeline with libFuzzer/AFL++ fuzzing gates) with human approval checkpoints.
github.comrepoPublished and added 7 May 2026🛡️ Security - GigaChad GRC
GigaChad GRC is a self-hosted, containerized Governance, Risk & Compliance platform covering compliance tracking, risk management, policy lifecycle, third-party risk management (TPRM), audit management, and a trust center/questionnaire module. It runs entirely via Docker Compose (Node.js/NestJS microservices, React frontend, PostgreSQL, Redis, Keycloak for SSO/RBAC with a dev-auth bypass, Traefik gateway), and is licensed under Elastic License 2.0 (free for internal use, not for resale as a hosted service).
github.comrepoPublished and added 6 May 2026🛡️ Security - n8n Cybersecurity Workflows
A GitHub repo of n8n automation blueprints for security teams, organized into Red Team/Pentest, Blue Team (SOC/DFIR/TI), AppSec/DevSecOps, and Platform/General categories. Each of the ~90 workflow ideas gives a Purpose, Integrations, and Flow Outline (e.g., subdomain recon hubs, attack-surface diffing, GoPhish campaign launchers, C2 event forwarding, phishing auto-triage, SAST-on-PR with Semgrep, DAST nightly with ZAP, container image policy gates, CVE prioritization with EPSS/KEV) that map to concrete n8n nodes and real security tools like Subfinder, Nmap, Shodan, Trivy, MISP, and VirusTotal.
github.comrepoPublished and added 6 May 2026🛡️ Security - Hawk-Eye
Hawk-Eye is a Python CLI tool that scans S3, MySQL, PostgreSQL, MongoDB, CouchDB, Google Drive, Slack, Redis, Firebase, GCS, and local filesystems for PII and secrets exposure. It uses OCR and text analysis to inspect documents (docx, xlsx, pptx, pdf), images, archives, and video files, with configurable regex fingerprints, Slack alerting, and JSON output for CI/CD integration.
github.comrepoPublished and added 6 May 2026🛡️ Security - Microsoft Agent Governance Toolkit
Agent Governance Toolkit (AGT) is a Microsoft open-source framework that intercepts every tool call, message, and delegation made by an AI agent in deterministic application-layer code before it reaches the model, enforcing YAML/OPA/Cedar policies, agent identity (SPIFFE/DID/mTLS), and tamper-evident audit logs. It ships SDKs for Python, TypeScript, .NET, Rust, and Go, a Claude Code plugin, and CLI tools (agt verify, agt red-team scan) for OWASP-style compliance checks and prompt-injection audits. The project explicitly frames prompt-level safety as insufficient, citing a 100% adversarial attack success rate on GPT-4o/Claude 3/Llama-3 (Andriushchenko et al., ICLR 2025) as motivation for application-layer enforcement instead.
github.comrepoPublished and added 6 May 2026🛡️ Security - requie/LLMSecurityGuide
A GitHub reference guide covering the OWASP Top 10 for LLM Applications 2025 and the OWASP Top 10 for Agentic Applications 2026 (ASI01–ASI10, released December 2025 at Black Hat Europe), with Python code samples for attacks (prompt injection, training-data extraction, RAG poisoning, agent goal hijacking, memory poisoning) and matching defenses (guardrails, memory integrity validation, tool-usage guards, zero-trust agent execution). It also curates red-teaming and guardrail tooling — garak, DeepTeam, Promptfoo, ARTKIT, Meta LlamaFirewall, LLM Guard, NeMo Guardrails, Amazon Bedrock Guardrails, Langfuse — plus an MCP security checklist and a security readiness checklist for LLM/agentic deployments.
github.comrepoPublished and added 5 May 2026🛡️ Security - zeroc00I/DontFeedTheAI
DontFeedTheAI is a transparent proxy built for pentesters that intercepts requests to LLM APIs (Claude Code, OpenAI SDK, OpenRouter, etc.), using a local Ollama-based detector plus regex to strip and surrogate real IPs, credentials, hostnames, and PII before the request leaves the machine, then restores the originals on the response. It ships a setup wizard for local Docker or VPS+SSH-tunnel deployment, a visual audit page for reviewing ORIGINAL→SURROGATE mappings, and an integration test suite (53 fixtures) to verify zero leaks across the full pipeline. The goal is to let engagements use cloud-quality LLM reasoning without ever sending real client data (org names, credentials, hostnames) to a third-party API.
github.comrepoPublished and added 5 May 2026🛡️ Security