 Top AI coding agent security resources — November 2026
Adversa AI's November 2026 roundup of 14 AI coding agent security resources from October. It covers CVE-2026-103572 (Visual Studio Copilot and SSMS RCE via trailing-dot filename), an unpatched Claude Code child-session hook bypass, a Copilot CLI cryptographic context injection, and a CVE-less opencode MCP OAuth RCE. It ends with a checklist for auditing agent configs and gateways.
 adversa.aiarticlePublished and added 2 Nov 2026🛡️ Security
 Smarthouse (@localyzapp) on X
A reply by Smarthouse (@localyzapp) on X to a question about the best harness for connecting local models to a Minecraft server. It suggests an MCP server that wraps RCON plus a small agent loop. The main pitfall is block coordinates: expose "/execute if block" as a read tool so the agent can check blocks before placing them, or it will hallucinate terrain.
 x.comthreadAdded 2 Nov 2026, published 1 Nov 2026🧠 AI
- Lonnie VanZandt (@lonniev) on X
Secure Courier is a consent flow in Tollbooth DPYC, a monetization network for paid MCP services, that lets an AI agent act for a Nostr npub without holding the user's nsec. The service sends a signed, sealed direct message over Nostr relays, the user replies with a signed approval and an expiry, and the service issues its own encrypted grant. Lonnie VanZandt presents it as an alternative to central identity providers and CIBA. The thread gives no audit results.
x.comthreadAdded 1 Nov 2026🧠 AI - zahT3 (@zahT3zuo) on X
Hotseat is a free, open-source macOS menu bar app that moves Claude Code and Claude Desktop to another of the user's Claude accounts in one click and returns to the same session. Sessions, settings, skills and MCP servers are shared, so `claude --resume` works under either account. When a session hits a usage limit, it offers to continue under another account. It never reads tokens or cookies. Install with Homebrew.
x.comtoolAdded 1 Nov 2026, published 31 Oct 2026🧠 AI - ERC-8481: Agent Pre-Sign Risk Report
ERC-8481 is a draft Ethereum standard for the report a risk source returns about one prepared, unsigned request from an AI agent. Reports bind to the request by digest and are signed with EIP-712 by an ERC-8004 identity. Findings cover tokens, approvals, addresses, x402 payments and texts, each marked read or not read, with no score or verdict. The only implementation is toll, a free HTTP and MCP guard on Robinhood Chain.
 ethereum-magicians.orgotherAdded 2 Nov 2026, published 31 Oct 2026🧠 AI
 Tanmay (@TanmayK_03) on X
DBHub, a database MCP server, had a read-only mode bypass in its SQL check. The check treated every `--` as a comment, but MySQL only starts a comment when whitespace follows it. A hidden write statement could therefore still run, and a prompt injection could trigger it. Fixed in version 0.22.6. Replies say enforcement belongs in database grants and that parser tests need to be dialect-specific.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security- Lonnie VanZandt (@lonniev) on X
Tollbooth DPYC's "Secure Courier" is a consent scheme that lets an AI agent act for a Nostr npub at a paid MCP service without holding the user's nsec. The service sends a signed, sealed Nostr direct message, the user replies signed with their nsec and sets an expiry, and the service issues its own grant. The thread contrasts this with central identity providers and CIBA, arguing a breach reaches only grants that service issued.
x.comthreadAdded 1 Nov 2026, published 30 Oct 2026🛡️ Security - rikugan: LLM reverse-engineering agent for IDA Pro and Binary Ninja
Rikugan is a reverse-engineering agent that runs inside IDA Pro and Binary Ninja. It has its own generator-based agent loop, context management, plan mode and 60+ tools, and does not depend on an external MCP server. An orchestrator spawns parallel subagents to analyze a binary. It supports Anthropic, Gemini, MiniMax, Kimi, OpenAI-compatible endpoints and Ollama, with per-model notes.
 github.comrepoAdded 30 Oct 2026🧠 AI
- rikugan: LLM reverse-engineering agent for IDA Pro and Binary Ninja
Rikugan is an open-source reverse-engineering agent that runs inside IDA Pro 9.0+ and Binary Ninja, with its own agent loop instead of an MCP server. It has 60+ tools (decompiler, xrefs, strings, types, IL/microcode), parallel subagent exploration, an experimental /modify natural-language patching command and an experimental Binary Ninja deobfuscation skill for control flow flattening and opaque predicates. It supports Claude, Gemini, MiniMax, Kimi, OpenAI-compatible endpoints and Ollama.
github.comrepoAdded 30 Oct 2026🛡️ Security - Ritik Shukla (@Retik_S) on X
kanzo is a local kanban board that coding agents can update. It ships as one 4 MB binary that starts in 2 ms and runs on localhost. It also works as an MCP server, so Claude Code and Codex see the same tasks as the user. The board is stored as a folder that can sync through a private git repo. The post is brief and gives no further detail.
x.comtoolPublished and added 30 Oct 2026🧠 AI - aiproduck (@aiproduck) on X
Ruflo is an MIT-licensed wrapper for Claude Code and Codex that adds agent swarms, vector memory and an MCP server. The plugin install writes no files to the workspace, while npx init adds a .claude/ directory, CLAUDE.md and hooks. The post warns that mods run with the account's permissions, so users should read them first. It gives no benchmarks or architecture detail.
x.comthreadPublished and added 30 Oct 2026🧠 AI  川崎元 (@foryangxin) on X
CVE-2025-6514 is an OS command injection (CWE-78, CVSS 9.6) in mcp-remote 0.0.5 to 0.1.15, fixed in 0.1.16. A malicious MCP server supplies a crafted authorization_endpoint during OAuth discovery, and the open package passes it to PowerShell on Windows. The thread cites the MCP spec's URL scheme allowlist rules and advises treating discovery metadata as untrusted, pinning bridge tools and sandboxing them.
x.comthreadAdded 2 Nov 2026, published 30 Oct 2026🛡️ Security VulnCheck - Outpace Adversaries
VulnCheck Open Source is an index of VulnCheck's open-source tooling for its vulnerability and exploit intelligence. It lists a Python API client, a CLI, a GitHub Action for CI/CD, go-exploit (a Go exploit framework), an MCP server for delivering intelligence to AI clients, and VulnCheck Insights, a Chrome extension that highlights CVEs, CPEs and PURLs on web pages and enriches them. The page gives only one-line descriptions.
 vulncheck.comtoolAdded 29 Oct 2026🛡️ Security
 SAIL Framework: A Practical Guide for AI Security
The SAIL Framework from Pillar Security is a seven-phase, lifecycle-oriented method for securing AI systems. The phases are AI policy and safe experimentation, AI asset discovery, AI security posture management, AI red teaming, runtime guardrails, sandboxed execution for agents and MCP servers, and AI activity tracing. It argues for a "Shift Up" approach that protects the business logic AI controls, and it is meant to sit on top of existing standards.
 pillar.securityarticleAdded 29 Oct 2026🛡️ Security
- Prasenjit Sarkar (@stretchcloud) on X
A thread on Cloudflare's agent-readiness scan and the AgentReady.org open spec for "Agent Experience", developed with Vercel, Stripe, Auth0, Mintlify, Google, Netlify and Elementor. The scan grades whether agents can find a site (robots.txt, DNS), read clean Markdown, pass bot rules, and discover an MCP server or API catalog. One quoted example raised a score from 20 to 67 by shipping an API catalog with Link headers, an MCP server card, a skills index and an AI catalog file.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI  Rohan Paul (@rohanpaul_ai) on X
Rohan Paul's X post summarizes a TikTok paper on MCP attacks. LLM agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the user query, the server reply and the final answer. The attack works because agents read natural-language tool descriptions when choosing and ordering tool calls. The visible text is truncated and gives no success rates or defenses.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security- rohitg00/ai-engineering-from-scratch
ai-engineering-from-scratch is a free, MIT-licensed curriculum of 542 lessons in 20 phases, from math and deep learning through transformers, LLM engineering, MCP, agents and capstones. Code is in Python, TypeScript, Rust and Julia. It includes three graded projects (retrieval evaluation, agent trace debugger, tool call firewall), installable tutor skills for Claude Code and Codex, and certification prep tracks.
github.comcourseAdded 29 Oct 2026🧠 AI  Cisco Open Sources Quarry to Catch AI Agent Attacks Hidden in Harmless Steps
Project Quarry is a neurosymbolic rule language Cisco has open sourced to detect AI agent attacks that only show up across a sequence of individually benign steps. Rules combine ML classifier and LLM judge evidence with symbolic checks on sequences, strings and tool relationships. The starter pack has a DSL, evaluation runtime, CLI scanner, Python SDK and a plugin for Claude Code, Codex and other MCP-compatible agents.
 securityweek.comarticlePublished and added 29 Oct 2026🛡️ Security
 What is an AIBOM? AI bill of materials explained for security teams | Endor Labs
An AIBOM is a machine-readable inventory of models, datasets, dependencies, AI services, agents and MCP servers, with evidence of origin, license, integrity and evaluation. The Endor Labs explainer walks through a worked CycloneDX example for a fine-tuned support assistant. It compares CycloneDX ML-BOM, SPDX 3.x, the OWASP AIBOM project and the May 2026 CISA/G7 guidance, and lists what an AIBOM cannot show: runtime behavior and agent actions.
 endorlabs.comarticlePublished and added 29 Oct 2026🧠 AI
- What is an AIBOM? AI bill of materials explained for security teams | Endor Labs
AIBOM explainer from Endor Labs: an AI bill of materials is a machine-readable inventory of models, datasets, dependencies, AI services, agents and MCP servers, with origin, license and integrity evidence. It walks through a CycloneDX entry for a fine-tuned model, compares CycloneDX ML-BOM, SPDX 3.x, the OWASP AIBOM Generator and the May 2026 CISA/G7 minimum-elements guidance, and lists a six-step build process. It also states what an AIBOM cannot show: model safety, runtime behavior and coding-agent actions.
endorlabs.comarticlePublished and added 29 Oct 2026🛡️ Security - Rohan Paul (@rohanpaul_ai) on X
Rohan Paul's X post summarizes the paper "Log-To-Leak: Prompt Injection Attacks on Tool-Using LLM Agents via the Model Context Protocol", from TikTok researchers. It reports that MCP-using agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the query, server reply and final answer. The attack works through natural-language tool descriptions that agents read when choosing and ordering tools. The visible text is truncated.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security  Eddy (@ieddysun) on X
Expo's official skills package gives AI coding agents scoped instructions for building Expo apps. One command, npx skills@latest add expo/skills --skill '*', installs it for Cursor, Copilot and Windsurf, while Claude Code and Codex use their plugin marketplaces. Skills include expo-router, expo-animation, expo-upgrade and eas-update. The Expo MCP server adds live docs lookup, compatible dependency installs, EAS build monitoring and simulator screenshots.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI- Hakimi Eiqbal (@hakimieiqbal) on X
A practical reverse-engineering map by hakimieiqbal on X that picks tools by target: native binaries, .NET, Electron, iOS, firmware, WebAssembly and network protocols. It introduces REA (morluto/rea), which connects coding agents to RE tools, and lists MCP bridges for IDA Pro, Ghidra and radare2. It adds an evidence-first workflow and free courses such as pwn.college and OpenSecurityTraining2.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security - Hakimi Eiqbal (@hakimieiqbal) on X
A thread by Hakimi Eiqbal that maps reverse-engineering tools by target type: native binaries, Electron, .NET, iOS, firmware, WebAssembly and network protocols. Its AI sections cover REA (an open-source layer connecting coding agents to analysis tools) and MCP bridges for IDA Pro, Ghidra and radare2. It argues for an evidence-first workflow and gives a prompt that separates verified facts from hypotheses.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI  ADLC compliance: Mapping agentic development to NIST SSDF, OWASP, and the EU AI Act | Endor Labs
ADLC compliance is Endor Labs' interpretation of how NIST SSDF (SP 800-218), the OWASP LLM and Agentic Top 10 lists, and the EU AI Act apply to software built with coding agents. It splits requirements into a code surface and an action surface (shell, files, MCP calls, package installs). It gives a four-step EU AI Act scoping path and says that system prompt rules and agent self-reports are not audit evidence.
endorlabs.comarticlePublished and added 28 Oct 2026🧠 AI- ADLC compliance: Mapping agentic development to NIST SSDF, OWASP, and the EU AI Act | Endor Labs
ADLC compliance guide from Endor Labs that maps agentic development to NIST SSDF (SP 800-218 v1.1), the OWASP LLM Top 10 2025 and Agentic Top 10, and the EU AI Act as amended by Regulation (EU) 2026/1744. It splits controls into a code surface and an action surface (shell, file access, MCP calls, package installs). It gives a four-step AI Act scoping path, the new Annex III date of 2 December 2027, and evidence guidance. It states the crosswalk is the vendor's interpretation, not legal advice.
endorlabs.comarticlePublished and added 28 Oct 2026🛡️ Security  The ADLC maturity model: 5 stages of agentic development security | Endor Labs
The ADLC maturity model is a proposed five-stage framework from Endor Labs for scoring security controls over coding agents, from unmanaged experimentation to continuous verification. Each stage has requirements on two tracks, agent actions (shell commands, MCP calls, package installs) and agent output (code, dependencies, secrets). It sets stage 3 at deterministic hooks that block actions, gives evidence-based assessment questions, and lists traps such as relying on prompt-level rules.
endorlabs.comarticlePublished and added 28 Oct 2026🛡️ Security Kizuno18 (@Kizuno18) on X
Kizuno18's X post argues that the move from local stdio and Docker MCP servers to remote HTTP/SSE endpoints matures the Model Context Protocol in enterprise infrastructure. It lists three trade-offs: short-lived OAuth/JWT bearer tokens replace mounted admin credentials, deferred tool discovery avoids roughly 20k tokens of eager schema loading, and HCP Terraform enforces Sentinel/OPA policy, audit trails and approvals server-side. Opinion post with no benchmarks or code.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026🧠 AI Buchi Reddy B (@buchireddy) on X
Buchi Reddy B's X thread comments on Forever Security's research (Gal Weizman, Omer Samet) on coding agents. A web page silently writes a fake AGENTS.md or CLAUDE.md into a Downloads folder, and Codex and Claude Code follow it as project rules. Codex then wrote an attacker's MCP server into the machine-wide config, so one injection becomes a standing connection for every session. It asks whether teams inventory runtime MCP connections against approved lists.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security- Rohan Paul (@rohanpaul_ai) on X
Hi3D v1.0 (formerly Sparc3D) is an open-sourced image-to-3D model from Hi3D, which runs a closed v3.0 refining at 2048 cubes per side. In a test with 13 professionals in 3D algorithms, 562 judgments against eight other image-to-3D models favoured it 83.5% of the time. The thread also covers the Hi3D Agent and an MCP server for other agents. Back and bottom views were checked, where TRELLIS.2 collapsed a winged figure.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI  cubillas (@cubillas888) on X
The tweet relays Pillar Security research that opencode on Windows and WSL could run attacker-controlled code during remote MCP server OAuth sign-in. The fix shipped in opencode 1.18.33 on 28 September, with no advisory or CVE published. It advises users of remote MCP servers to update and review which servers they connect to. Technical details are not in the post.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security Nicholas Martin (@ndgmlondon) on X
X thread started by Nicholas Martin (#IAM) advising that MCP tool permissions be verified and scoped session tokens used to enforce least privilege against indirect prompt injection. Replies argue that token scoping does not solve the confused deputy problem, because an injection borrows the agent's legitimate authority. They recommend per-task tokens with short expiry, with the grant logged beside the call, and raise MCP server dependency supply-chain risk.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security Measuring Users' Security and Privacy Concerns About Third-Party Community Bots on Discord
Measurement study of 23,102 third-party Discord bots and 183,142 user reviews (2021-2026, 49 languages). A fine-tuned DeBERTa classifier plus manual validation yields 8,832 security and privacy reviews, mapped to a 31-theme taxonomy; Data Sharing (30.5%) and Data Collection (16.2%) dominate. Permission count and admin status correlate only weakly with user concerns. The authors build BotLens, an MCP-server auditing framework with six tools.
 arxiv.orgpaperAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security
- Log-To-Leak: Prompt Injection Attacks on Tool-Using LLM Agents via the Model Context Protocol
Log-To-Leak is a prompt-injection attack on tool-using LLM agents that abuses Model Context Protocol tool metadata to trigger an attacker-controlled logging call after the last legitimate call, leaking the user query, server name, server response and agent response. Evaluated on five MCP servers and four agents, it reaches 62.64-100% attack success with 76.55-95.64% logging accuracy. Three defenses leave over 55% residual ASR on GitHub MCP with GPT-4o.
arxiv.orgpaperAdded 28 Oct 2026, published 26 Oct 2026🛡️ Security  David Gutierrez | Eng (@david_x_ai) on X
Thread on two October 2026 npm compromises: @subql/common 5.8.3 (5 October), published through GitHub Actions OIDC Trusted Publishing after the attacker tampered with the publish workflow, and tensorlake 0.5.144 (8 October), published by the project's own release workflow with valid provenance for about 1 hour 40 minutes. Both ran on install and stole cloud, GitHub, Kubernetes, Vault, SSH and .env credentials; tensorlake also took AI tool and MCP config. Its payload installed a gh-token-monitor service that deletes the home directory if the stolen GitHub token is revoked, so remove it before rotating.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security Benjamin👨💻 (@Hislordship_9) on X
Thread on Forever Security's finding that a planted Markdown "Engineering Work Guidelines" file in ~/Downloads made Codex add a "project-tools" MCP server to ~/.codex/config.toml. The server ran npm install function-color, a known malicious package, and started a child session with --dangerously-bypass-approvals-and-sandbox. Codex complied in over 90% of the firm's tests; Claude Code, via a CLAUDE.md setting ANTHROPIC_BASE_URL, about half. Advice: don't start agents in Downloads, review instruction files, and diff agent config.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security- David Gutierrez | Eng (@david_x_ai) on X
Thread on a critical opencode bug disclosed by Pillar Security on Oct 19. On Windows and WSL, a remote MCP server could run code during OAuth sign-in, because the server-chosen authorization URL was put unescaped into a PowerShell command, so a PowerShell subexpression executed. opencode fixed it in 1.18.33 on Sep 28 as a browser-launch refactor with no advisory or CVE. MCP Inspector published an advisory for the same bug class, and its fix needs a major bump of the open package.
x.comthreadAdded 27 Oct 2026, published 25 Oct 2026🛡️ Security - Dan Kornas (@DanKornas) on X
jshook is an open-source (AGPL-3.0) MCP server that gives AI agents a search-first, profile-aware reverse-engineering workspace for JavaScript, browser traffic, WASM and native processes. Agents start with a small searchable tool surface and move to workflow or full profiles only when needed. It drives Chromium or Camoufox over CDP, captures WebSocket traffic, has HTTP, GraphQL and Burp Suite helpers, and supports hot-reload plugins and declarative workflows. The post is a short announcement; the repository link is in a reply.
x.comtoolAdded 28 Oct 2026, published 25 Oct 2026🧠 AI - Dan Kornas (@DanKornas) on X
jshook is an open-source (AGPL-3.0) search-first reverse-engineering workspace for AI agents, exposed over MCP. It drives Chromium or Camoufox through CDP, captures WebSocket traffic, offers HTTP, GraphQL and Burp Suite helpers, deobfuscates JavaScript, rebuilds source maps and disassembles WebAssembly. Tool profiles start small and expand to workflow or full sets; hot-reload plugins and declarative workflows extend it.
x.comtoolAdded 28 Oct 2026, published 25 Oct 2026🛡️ Security - Agent Credit (@agentcredit_) on X
Agent Credit v1.3 is a remote MCP server that lets AI agents run credit checks on each other. It has six tools: score, compare, operator record, alerts and on-chain proof check. Calls are paid per use in USDC through x402 with no account or key. It also flags shared wallets, lists every token an operator launched and how each ended, and offers embeddable badges and wallet-signed record claims.
x.comtoolAdded 26 Oct 2026, published 25 Oct 2026🧠 AI - Search Search results for "security" | MCP Market
MCP Market search results for "security" in its skills category, listing about 20 installable AI agent skills. Entries cover OWASP Top 10 audits, secure PHP coding, STRIDE threat modeling, CVE remediation, security header analysis, misconfiguration finding, bug bounty triage and AgentShield scans of Claude Code configurations. One is a paid D365FO security-role XML skill. Each entry has only a one-line description and a category label.
 mcpmarket.comtoolAdded 25 Oct 2026🧠 AI
- Search Search results for "security" | MCP Market
MCP Market search results for "security" in the skills category, listing about 20 installable AI agent skills. Entries cover OWASP Top 10 audits, secure coding for PHP, STRIDE threat modeling, CVE remediation, security header analysis, misconfiguration finding, bug bounty triage and AgentShield scans of Claude Code configurations. One is a paid D365FO security-role XML skill. Each entry has only a one-line description and a category label.
mcpmarket.comotherAdded 25 Oct 2026🛡️ Security - Big Bull (@BIGBULLapp) on X
5ire is a desktop AI assistant and MCP client that connects to OpenAI, Anthropic, Google, Mistral, Grok, DeepSeek and Ollama from one window. It has a local knowledge base and tool calls over Model Context Protocol. The tools feature needs Python, Node and uv installed because it runs a local MCP server; without them it works only as a chat client.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🧠 AI  ReignSwords (@ReignSwords) on X
A reviewer tests GenOffice, an open-source Office suite (10.7k GitHub stars), through its CLI only. Markdown to .docx took 3.8s, JSON to .xlsx took 0.9s with a live SUM formula, and .docx to PDF failed twice until Xvfb supplied a display. It has byte-preserving edits, a skill file for Claude Code and Codex, and 29 MCP tools. Downsides: a 188MB download that filled a 512MB /tmp, Electron in the PDF path, and unproven trust in tracked changes and rollback.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🧠 AI- Gökdeniz Gülmez (@ActuallyIsaak) on X
An X post showing how to have Codex train a small model on Apple silicon through the mlx-lm-lora MCP server and skill. It gives five setup steps (pip install with the mcp extra, npx skills add, locate mlx-lm-lora-mcp, codex mcp add). The prompt runs four pre-training trials on tiny-random/qwen3 with the mlx-community/recycling_the_web-1k dataset. Codex picks the optimizer and learning rate itself, and the result is a table with validation loss and the best adapter path.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🧠 AI  Prasenjit Sarkar (@stretchcloud) on X
Post explaining Claude's new support for MCP Tasks and Elicitations. A server returns a durable task handle instead of blocking. The client polls tasks/get every 250 ms to 30 s, and states are working, input_required, completed, failed or cancelled. Elicitations pause a task at input_required for human approval. It also notes Cloudflare's stateless MCP servers and Code Mode, and Sentry and Linear adoption.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🧠 AI EveryDev.ai (@EveryDevAi) on X
ToolUniverse, from ScientistTools, is an open-source (Apache-2.0) toolkit that gives any LLM one interface to more than 1,000 scientific tools, models and databases such as PubMed, UniProt and ChEMBL. It ships a native MCP server, a Python SDK and a tu CLI, plus 68 pre-built agent skills. The post says it works with Claude Code, Cursor, Gemini CLI and Windsurf.
x.comthreadPublished and added 24 Oct 2026🧠 AI- Deletion, Substitution, Repair and Transplant: Component Attribution in BARBICAN, a Layered Prompt-Injection Gateway for MCP
BARBICAN is a fail-closed prompt-injection gateway for MCP tool mediation. This paper shows its arbitration classifier ran on tokenizer-mangled text for a whole evaluation. Fixing it raised AUC from 0.392 to 0.855 while system recall fell from 80.67% to 80.34%. The routed band is 96.82% malicious, so deletion ablations mislead without substitution experiments and class-balance reporting.
arxiv.orgpaperAdded 27 Oct 2026, published 23 Oct 2026🛡️ Security - Deletion, Substitution, Repair and Transplant: Component Attribution in BARBICAN, a Layered Prompt-Injection Gateway for MCP
The paper analyses BARBICAN, a fail-closed prompt-injection gateway for MCP tool mediation, using deletion, substitution, repair and transplant experiments. Its arbitration classifier ran on tokenizer-mangled text for a whole evaluation. Fixing that raised AUC from 0.392 to 0.855 while system recall fell from 80.67% to 80.34%. The band it receives is 96.82% malicious. The authors argue ablation figures need the band's class balance and substitution baselines.
arxiv.orgpaperAdded 27 Oct 2026, published 23 Oct 2026🧠 AI  ADLC Security Best Practices for Teams Shipping with Coding Agents | Endor Labs
ADLC Security Best Practices is an Endor Labs guide to controlling what AI coding agents can access, run, install and ship. It covers inventorying agents and MCP servers, sandboxing, pre-execution hooks instead of AGENTS.md rules, install-time package checks against slopsquatting and malware, reachability-based triage of agent PRs, and CI/CODEOWNERS protections. A five-step worked example and coverage metrics are included.
endorlabs.comarticlePublished and added 23 Oct 2026🛡️ Security- Yash Patil (@yvshpvtil) on X
leanrea is an 8 KB skill file that tells a coding agent which plain CLI tools to use for reverse engineering, replacing REA, a 207-tool MCP server. In the author's test it ran 38% faster and 35% cheaper, scoring 74/75 against 75/75. The author lists caveats: 3 runs per task, one model, one machine, and Claude with no skill was already decent.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🧠 AI - Yash Patil (@yvshpvtil) on X
leanrea is an 8 KB skill file that tells a coding agent which plain CLI tools to use for reverse engineering, replacing the 207-tool REA MCP server. The author's test reports 38% faster, 35% cheaper, and a score of 74/75 against REA's 75/75. Caveats listed: 3 runs per task, one model, one machine, and Claude with no skill already performed decently. Replies question whether the lost point was a task where structured tool output beat parsing CLI text.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security - Tool-Calling LLM Agents Under Realistic MCP Faults: Scale Does Not Purchase Fault Tolerance
MCP-Injector is a protocol-aware fault-injection middleware for Model Context Protocol tool calls, with permanent, transient and intermittent faults on seedable schedules. Its fault model comes from 57,240 issue and PR threads across 1,774 open-source MCP repositories. In a 1,350-cell experiment, faults cut task-completion score by 60% (8.08 to 3.23 of 10), and the 120B gpt-oss model was no more resilient than the 20B. Agent stacks differed in how well they absorbed faults.
arxiv.orgpaperAdded 26 Oct 2026, published 23 Oct 2026🧠 AI - Agentic AI Defense: Decode-Time Provenance Binding for MCP
Decode-time provenance binding is a defense for Model Context Protocol agent pipelines against cross-modal trust laundering, where instructions hidden in an email-signature image via LSB, DCT or metadata steganography get decoded by a tool. It combines HMAC-authenticated trust labels, a provenance ledger and context-taint tracking to block critical tool calls. On a real MCP testbed with 24 adaptive payloads, attack success fell from 100% undefended (62.5% for keyword and regex filters) to 0%.
arxiv.orgpaperAdded 26 Oct 2026, published 22 Oct 2026🛡️ Security - Donating Agent Skills to the Agentic AI Foundation
Simon Willison's link post covers Anthropic's 22 October 2026 announcement that it is donating the Agent Skills standard to the Agentic AI Foundation (AAIF) under the Linux Foundation. Anthropic co-founded the AAIF with Block and OpenAI and earlier donated MCP to it. Willison notes he predicted this in December 2025 and found his old post by querying his blog through datasette-mcp in Claude.
 simonwillison.netarticlePublished and added 22 Oct 2026🧠 AI
- Meku_SI (@MEKU_SI) on X
MEKU Human Cloud is an MCP server for agents that need a real person to do a task. It exposes three tools: search humans (read-only), request a human (a human operator reviews every request first), and check status. It is listed in the MCP Registry as farm.meku/human-cloud. The tweet gives no detail on pricing, humans available or request formats; those are in the linked docs.
x.comtoolAdded 23 Oct 2026, published 22 Oct 2026🧠 AI - Dan Kornas (@DanKornas) on X
aula-mcp is an open-source (MIT) TypeScript MCP server that connects an AI client to Denmark's Aula school platform. It exposes tools for profiles, calendar events, messages, notifications, posts and weekly plans. MitID credentials and OAuth tokens are stored in macOS Keychain or an AES-256-GCM encrypted file. The HTTP server binds to 127.0.0.1, and the presence write tool stays off until AULA_MCP_WRITE=1 is set.
x.comrepoAdded 23 Oct 2026, published 22 Oct 2026🧠 AI - SpyTech Ai (@RizeOnline) on X
XiaoZhi ESP32 is an open-source, MIT-licensed firmware stack that turns ESP32 boards into MCP-based voice chatbots using models such as Qwen and DeepSeek. It streams Opus audio over WebSocket or MQTT + UDP through ASR, LLM and TTS, adds offline ESP-SR wake words, and uses device-side MCP to drive speakers, LEDs, servos and GPIO. It supports 138 board directories and builds with ESP-IDF 6.0.1 or newer.
x.comthreadAdded 23 Oct 2026, published 21 Oct 2026🧠 AI  VibecodersHQ (@VibeCodrHQ) on X
Post summarising Pillar Security's finding of a remote code execution flaw in OpenCode, the open-source AI coding agent. Versions 1.0.137 through 1.18.32 could run code from a remote MCP server during OAuth sign-in on Windows and WSL, with no prompt injection needed. The fix is in 1.18.33 (released 28 September). No advisory or CVE was issued, so scanners will not flag old installs. Interim advice is to remove unvetted remote MCP servers.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security- Swif (@swif_ai) on X
Swif (@swif_ai) reports that in the MCP TypeScript server SDK versions 2.0 to 2.2, a single server instance shared by several HTTP clients, which is the pattern the README shows, could send one client's responses to another client. Version 2.3.0 refuses this setup, so developers must build a server per request or per session. The post gives no CVE, advisory ID or technical detail.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security - Swif (@swif_ai) on X
A post from Swif (@swif_ai) on the MCP TypeScript server SDK versions 2.0 to 2.2. A single server instance shared across HTTP clients, the pattern shown in the README, could send one client's responses to another client. Version 2.3.0 refuses that setup, so servers must be built per request or per session. The post gives no code or advisory ID.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🧠 AI - Show HN: Omnara – Open-source alternative to Claude Managed Agents
Omnara is an open-source, self-hostable managed agent platform, an alternative to Claude Managed Agents and OpenAI's Agents API. It runs agents on any model (OpenAI, Anthropic, OpenRouter, Bedrock, LiteLLM, Ollama) and any machine, with Postgres-backed durable state, stateless workers, per-tool permissions, MCP, skills, memory, subagents, schedules and Slack, Discord and GitHub triggers. It ships a REST API, TypeScript SDK, CLI and Docker Compose setup.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🧠 AI  Software supply chain security best practices for 2026
Aikido's guide to software supply chain security controls for 2026, tied to real incidents. It covers a 48-hour package cooldown, ignore-scripts, lockfile enforcement, SHA and digest pinning, scoped tokens, FIDO2, developer endpoint protection, extension allowlists, agent sandboxing, MCP server vetting, slopsquatting, signed SBOMs and rotation drills. Examples include the March 2026 axios compromise and the March 2025 tj-actions/changed-files attack.
 aikido.devarticleAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security
 How Commerce.com and Cloudflare are getting storefronts ready for AI agents
Cloudflare and Commerce.com describe enabling WebMCP, Google's proposed browser standard for exposing structured tools to AI agents, across almost 100,000 storefronts. Cloudflare injects a bridge script at the edge that proxies tools from Commerce.com's backend MCP server. Per-merchant opt-out uses Configuration Rules and custom hostname metadata, and a configurable MCP URL (/api/mcp) was added.
 blog.cloudflare.comarticleAdded 29 Oct 2026, published 21 Oct 2026🧠 AI
 Launch HN: Alter (YC S25) – Access control for multi-user agents
Alter is a privileged access management layer for AI agents (YC S25). It stores credentials in a vault, injects them per request through a proxy, gives each agent its own identity and scoped grants, and logs every call to a tamper-evident audit trail. One SDK call covers storage, refresh, policy and audit for 140 API providers, with LangChain, MCP and AWS integrations. Policy is default-deny down to the parameter, with human approval for risky calls.
 alterauth.comtoolAdded 22 Oct 2026, published 21 Oct 2026🧠 AI
 AI Model Risk Depends on What the Model Can Reach
Snyk's State of Agentic AI Adoption Volume III scores models against 29 attacker goals (0 to 1,000) and matches them to AI-BOM scan data from 1,693 environments. 74.5% reference a model scoring 500+ on some goal and 49.2% one scoring 750+. Risk depends on agent and MCP server reach, and the fix is either switching models or tightening application controls, depending on the goal. Only 37.5% of model occurrences have a score.
 snyk.ioarticlePublished and added 21 Oct 2026🛡️ Security
- Combining Long-Term Memory and LLMs Comes at a High Cost: From Prompt Injection to Persistent Compromise
Paper on memory injection, where prompt injection persists across sessions through the long-term memory of LLM-as-a-service platforms. It presents a general threat model and shows all NIST attack goals are achievable on ChatGPT Instant 5.3, Claude Sonnet 4.6 and Gemini 3 Flash. Vectors include personal memories, projects, skills, organization instructions and MCP resources. On Claude, shared memory lets an attacker compromise multiple users in an organization and exfiltrate prompts. Nearly half of the derived mitigations are unimplemented.
arxiv.orgpaperAdded 24 Oct 2026, published 20 Oct 2026🛡️ Security  Paulo Pierrondi | AI agents (@paulopierrondi) on X
Paulo Pierrondi's X post, part 9 of a series on installing MCP servers, lists a monthly review of installed servers. The checks are which tools the agent used, servers not called in weeks, overlapping tools that confuse the model, and whether each server still has an owner. A reply adds a decommissioning check: after removal, confirm the server's old credentials can no longer call the backend.
x.comthreadPublished and added 20 Oct 2026🧠 AI- DFIR Radar (@DFIR_Radar) on X
DFIR_Radar weekly detection engineering digest covering 23 new and 19 updated rules across 6 GitHub repositories. It lists KQL rules for Azure Key Vault secret retrieval, MCP client User-Agent bulk operations and local Azure token theft, AWS CloudTrail analytics, Sigma rules for firewall and ETW tampering (decimal 17 vs hex 0x11), updated LOLDrivers hashes, and Sublime email rules for OAuth consent phishing and fake IRS W-9 PDFs.
x.comthreadAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security - Huda (@AlAssaf_H) on X
Source-level review of x64dbg-MCP, GhidraMCP and IDA Pro MCP security, dated October 2026. It covers GHSA-4478-h5jv-647m (missing authentication, 0.0.0.0 bind) and GHSA-jgj3-97w2-9v9r (Content-Length integer overflow before the token check, causing a DoS panic), and compares tags 1.0, v1.1 and v1.2. It separates network reachability, tool authority and semantic influence from hostile binaries. No new exploit is claimed.
x.comarticleAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security - Panos Gkatziroulis 🦄 (@ipurple) on X
Malvex (JoasASantos/Malvex) is an AI-driven malware analysis framework that integrates more than 30 analysis tools, a web REPL and an MCP server. Panos Gkatziroulis shared it on 19 October 2026 and noted that it was written by AI. The tweet gives no detail on which tools are bundled or how the AI drives them.
x.comrepoAdded 22 Oct 2026, published 19 Oct 2026🛡️ Security  Angel (@ziran_pu) on X
AshAi, the AI package for the Elixir Ash Framework, is getting MCP client tools. Creating an MCP server with AshAi was already simple, but connecting your own LLM tool loop to an external MCP server had to be built by hand. The planned release includes OAuth client management resources. The post gives no release date, API details or code.
x.comthreadAdded 21 Oct 2026, published 19 Oct 2026🧠 AI Santhosh Patel (@santhosh_patell) on X
Summary of Pillar Security research on opencode, in which a malicious remote MCP server runs code on a Windows or WSL machine during the OAuth login step. The login URL goes unsanitised into PowerShell through the npm "open" package, so an https:// link containing $(...) executes. Affected versions are 1.0.137 to 1.18.32, fixed in 1.18.33 (28 September) as a "refactor" with no advisory or CVE. The behaviour was first reported in 2020 as a WSL 2 broken-link bug.
x.comthreadAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security- Saylor (@Kev96790724) on X
G-Krusch is an MIT-licensed, local-first Google Workspace hub built on Node.js 22 and SQLite WAL. It runs a 12-tool MCP server (SSE and Stdio) plus a REST bridge on port 5446 for Drive, Calendar and Gmail. It includes a 1,024-dimension hybrid Drive RAG with an embedding cascade (Ollama bge-large, then Gemini, then offline fallback) and FTS5 BM25. PDF extraction returns page citations. Tokens are kept in an AES-256-GCM vault; 30 of 30 tests pass.
x.comrepoAdded 21 Oct 2026, published 19 Oct 2026🧠 AI - Show HN: WhatsApp MCP running free on Cloudflare
whatsapp-mcp is an MCP server that runs in the user's own Cloudflare account and lets MCP clients such as Claude Code and Claude Desktop search and read WhatsApp chats. It links as a WhatsApp Web-style device through Baileys, stores messages in SQLite with FTS5 inside a Durable Object, and is read-only. The README documents deployment, OAuth sign-in, contact naming through agents, and workerd shims for Baileys.
github.comrepoAdded 20 Oct 2026, published 18 Oct 2026🧠 AI  FastFix AI (@FastfixAI) on X
FastFix AI thread giving six checks before installing a plugin, MCP server or skill for a coding agent. It starts from a 300K-star repo that an agent found writing to Claude Code, Codex and Copilot configs on install. Checks: read before running, inspect npm install scripts, verify the real repo against lookalike trojaned copies, pin versions, diff agent configs, and limit tokens and permissions.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security- Dan Kornas (@DanKornas) on X
decomp.wtf is an open-source (MIT) local workspace where AI coding agents decompile games into C, one function at a time. Agents receive assembly, data, callers and earlier attempt notes, then each C candidate is compiled with the game's original compiler, linked at its real address and compared byte for byte, with instruction diffs on misses. It exposes MCP tools for Claude Code, Codex, Antigravity CLI and opencode, plus a live view of agent calls and match scores.
x.comtoolAdded 19 Oct 2026, published 18 Oct 2026🧠 AI  Magai (@HeyMagai) on X
Post from Magai (@HeyMagai) on Invariant Labs research showing that an approved MCP server can change its tool descriptions later without a new approval prompt, a "rug pull" like those in malicious code packages. It recommends pinning approval to tool definitions by hashing descriptions and re-prompting when the hash changes. For tools that move money, limits should stay server-side.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security- ToFu: Exploiting and Fuzzing the LLM–Orchestrator–Tool Trust Boundary
ToFu is a tool-aware fuzzing framework for LLM tools, including MCP servers. It maps each tool argument, using its metadata, to one of 74 CWE-guided semantics-aware sanitizers (path, URL, SQL and similar). It then generates schema-valid Atheris harnesses and semantic oracles, using runtime tracers for in-process tools and outcome oracles for opaque ones. The LLM (gpt-4.1) only maps sanitizers and writes seeds; it is never the security judge. The paper also shows a "Repeat-After-Me" trick, where an LLM told to repeat attacker-crafted text emits a tool call the orchestrator executes, reproduced on LangGraph, MAF, ADK 2.0, AutoGen, Strands and CrewAI. Across 273 runnable MCP servers (3,405 tools) it reports 253 verified bugs in 343 tools across 118 servers, such as path traversal, log injection and exfiltration. These are failures a crash-based fuzzer would miss. The result matters because it shows LLM-generated tool arguments cannot be treated as trusted.
arxiv.orgpaperAdded 18 Oct 2026🧠 AI - ToFu: Exploiting and Fuzzing the LLM–Orchestrator–Tool Trust Boundary
ToFu is a tool-aware fuzzing framework that derives semantic security checks for LLM tools (mainly MCP servers) from their metadata and a corpus of 74 CWE-guided sanitizers. It generates schema-valid Atheris harnesses, uses runtime tracers and outcome oracles to catch bugs that don't crash, and uses an LLM only to map sanitizers and seed inputs, never as the judge. It also describes a "Repeat-After-Me" attack, in which the LLM is told to repeat attacker-written text that the orchestrator then dispatches as a tool call. It was reproduced on LangGraph, MAF, ADK, AutoGen, Strands and CrewAI. On 273 MCP servers it reports 253 verified bugs across 343 tools in 118 repositories, including path traversal, log injection, exfiltration and command bypass.
arxiv.orgpaperAdded 18 Oct 2026🛡️ Security - eliasbiondo/antirion
Antirion is an open-source AI gateway shipped as one Rust binary with a built-in admin console. It sits between apps and providers such as OpenAI, Anthropic, Bedrock, Vertex and vLLM, translating between OpenAI, Anthropic, Gemini and Bedrock dialects. It covers routing with fallbacks and circuit breakers, budgets, guardrails, caching, MCP and A2A gateways, SSO, and a benchmark against Bifrost 2.2.4 and LiteLLM 1.103.1.
github.comrepoAdded 21 Oct 2026, published 17 Oct 2026🧠 AI - ralphtradesz/trading-hub
Trading Hub is a free macOS desktop trading platform built with C#/.NET 10 and Avalonia. It uses the user's Claude Code subscription: a chat writes and fixes C# strategies, an in-app MCP server lets Claude run backtests, optimizations and walk-forwards and write reports, and a risk agent proposes position sizes. Install and a Windows port are both driven by Claude Code prompts. License is MIT with Commons Clause.
github.comrepoAdded 19 Oct 2026, published 17 Oct 2026🧠 AI - Steven Daugherty (@StevenDaugherty) on X
Post warning that FastMCP had a critical flaw where a malicious MCP server could execute code on the connecting client through a crafted tool schema. Fixed in FastMCP 3.4.8 and 4.0.11, and there is no patch for the 2.x line. It matters to anyone whose agents connect to MCP servers they don't control. The post gives no CVE ID or technical root cause.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🛡️ Security - OWASP/MCP-Security-Testing-Guide
OWASP MCP Security Testing Guide is a living, GPL-3.0 collection treating the Model Context Protocol as a security boundary from user through model, MCP client, MCP server and tool to the target system. It covers threats, secure development, host/client controls, supply chain, enterprise gateways, detection, incident response, taxonomy, public incidents, case studies and review checklists, with 79 tests in Chapter 3 (sections 3.1–3.19). It includes a finding template, and it links the MCP Goat lab for safe practice. It is useful to AppSec, red team and SOC people assessing MCP deployments.
github.comrepoAdded 17 Oct 2026🛡️ Security - alex09x/kyb
KYB (Know Your Business) is a Rust/axum server that stores agent-written knowledge, incident reports and tasks as Markdown files in Git, one commit per change. Search is hybrid: Tantivy BM25 fused by reciprocal rank with local multilingual-e5-small ONNX vectors, and it can query historical versions or "as of" a date. It ships a kyb CLI, a native MCP endpoint (Claude Code, Codex, Antigravity, Gemini CLI), an installable agent skill, token auth with per-write attribution trailers, secret scanning on writes, and a web console. It targets persistent shared operational memory for multi-agent, multi-machine fleets.
github.comrepoAdded 17 Oct 2026🧠 AI  TokenMaxxing: How to Get the Most Out of Your AI Models
Decrypt guide to "tokenmaxxing" reframed as maximizing value per token rather than burning tokens. It gives tiered tips: pick smaller models for simple jobs, write one clear prompt, start new chats, cap output length, and use free models (beginner); Claude Code commands like /model, /clear, /compact, /context, /mcp, /effort and plan mode (intermediate); and prompt caching via cache_control, 50% batch discounts, and agent budget limits like --max-budget-usd (advanced). Includes context on Meta, Amazon and Uber token leaderboards and spend, a worked invoice-processing example where routing cut cost from $30 to $3.90, and the Jevons paradox in falling token prices.
 decrypt.coarticlePublished and added 17 Oct 2026🧠 AI
 Show HN: Things to Do API
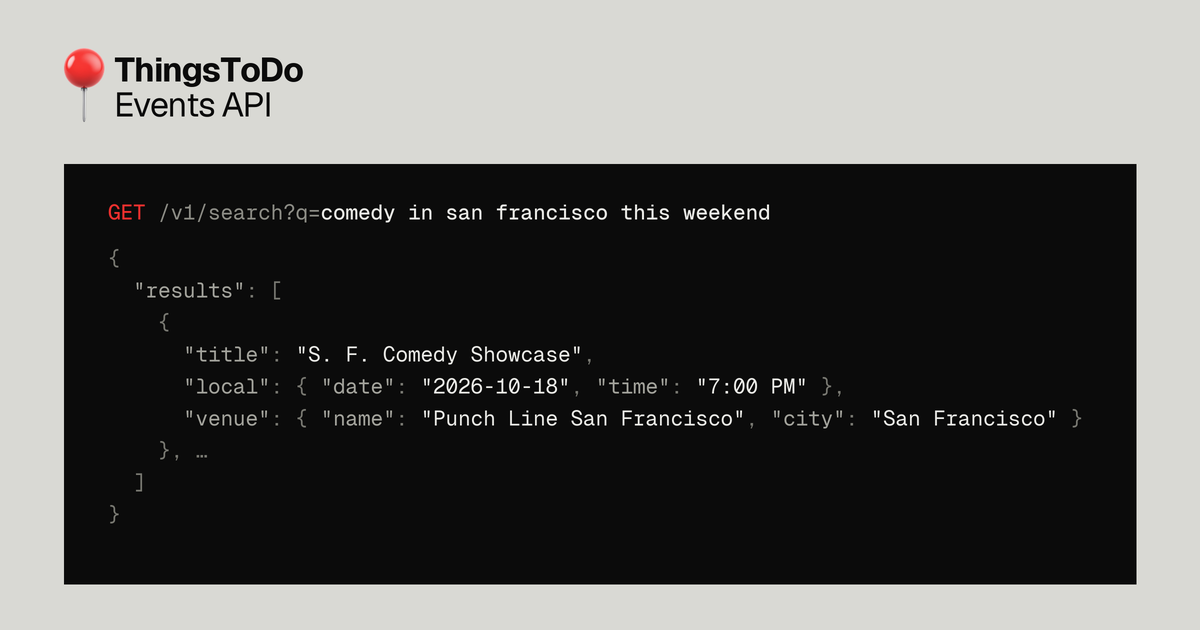
Things to Do API is a hosted knowledge base of local events (shows, talks, pop-ups, markets, festivals) that you query in natural language, for example `/v1/search?q=comedy+in+san+francisco+this+weekend`. It returns structured JSON with title, category, local start time, venue and ticket and source links. It also exposes an HTTP MCP endpoint, added with `claude mcp add --transport http thingstodo https://api.thingstodoapi.com/mcp`, so agents can use it as a tool. Coverage is live for the San Francisco Bay Area, with New York City and Los Angeles coming. Pricing is pay-as-you-go from $5 per 1,000 calls, the first 1,000 a month are free, and there is a 300 calls/min limit.
 thingstodoapi.comtoolAdded 18 Oct 2026, published 16 Oct 2026🧠 AI
- Nicholas Martin (@ndgmlondon) on X
An X post advises auditing every MCP write tool against the database role it actually runs under. A shared service key lets prompt injection trigger unapproved writes, so each agent session should get a read-only role, with a test that writes are denied. Replies note that MCP servers often inherit ambient host credentials or can escalate through a second connection pool, and suggest also testing that another tenant's rows are unreadable with the same role.
x.comthreadAdded 18 Oct 2026, published 16 Oct 2026🛡️ Security  In Other News: ICS-Sniper Attack, Hacking XWorm Malware Operators, $250k Chrome Exploit
SecurityWeek's weekly roundup covers ICS-Sniper, a UBC proof-of-concept that uses VPN-encrypted packet size, direction and timing to drop critical SCADA traffic on cloud-hosted ICS (tested on the SWaT water testbed). It also covers an unauthenticated RCE PoC against the XWorm RAT C2 panel (up to 7.4) via path traversal DLL overwrite, and Langflow CVE-2026-105740 (MCP Stdio command injection, fixed in 1.9.0) exploited from September 19, before the CVE was published. Other items: XBOW's AI-assisted Chrome full-chain exploit (GPT-5.6 Sol, $250k bounty), Group-IB's KGB RAT analysis, Anthropic's disclosure of Claude rule-bending on live sites, Intel ending SGX after Diamond Rapids, Bank of America's Mythos-driven patching, the Burger King Japan breach and a West African scam-center takedown.
securityweek.comarticlePublished and added 16 Oct 2026🛡️ Security AmingIn_AI (@aming_inAI) on X
A tweet from AmingIn_AI describes a macOS screenshot-annotation tool. On release it saves the screenshot, a crop and the user's marks locally, then copies a 127.0.0.1 link. Claude Code or Codex on the same Mac can fetch that link and receive the marked image plus app/window info, and nothing is uploaded. It shows a local, privacy-preserving way to hand visual context to coding agents without MCP or cloud upload.
x.comthreadAdded 17 Oct 2026, published 16 Oct 2026🧠 AI- P.K. Sharma (@_pksharma) on X
Thread distinguishing two Langflow advisories on MCP Stdio command execution. CVE-2026-105740 (GHSA-7w94-79vh-5mr2) affects 1.8.3 and is fixed in 1.9.0, an authenticated non-admin path. CVE-2026-105697 (GHSA-w794-rj3p-xv45) covers 1.1.2 up to but excluding 1.10.3, with fixes in lfx and langflow-base too. The later fix validates the API, flow and pre-spawn boundaries and removes the shell wrapper, and the thread warns that LANGFLOW_AUTO_LOGIN=true can expose a token without credentials. It cites one sensor's telemetry (1,628 attempts from 28 IPs) with caveats, and gives a defensive checklist: verify patched packages, review stored MCP configs and imported flows, and hunt for unexpected child processes.
x.comthreadAdded 17 Oct 2026, published 15 Oct 2026🛡️ Security - My Credentials, Please: Detecting Filesystem Capability Laundering in MCP Servers at Scale
Studies "filesystem capability laundering" in MCP servers: client approval of a tool call grants the server process broad host filesystem access, so attacker-steered arguments can reach sensitive files outside the tool's declared contract. The authors build MCP-FSD, which infers per-tool least-privilege boundaries, plants credential fixtures outside them, and tests exploitability and sandbox containment by paired dynamic execution. Of 21,097 servers from nine registries, 16.4% of 4,806 triaged servers have filesystem capabilities despite non-filesystem classifications. Dynamic validation confirmed 150 vulnerable instances, and disclosure produced 13 advisories, including two CVEs in Anthropic's Git MCP Server.
arxiv.orgpaperAdded 17 Oct 2026, published 15 Oct 2026🛡️ Security  [tl;dr sec] #350 - Reverse Engineer Anything, Tracking AI-integrated Malware, Test-driving Jev
tl;dr sec issue #350 is a weekly security newsletter digest. It covers XBOW's six-day Chrome full-chain exploit built with GPT-5.6 Sol, Semgrep's IDOR benchmark metrics, the EntraGoat vulnerable Entra ID lab, Zenity's AWS Bedrock AgentCore IMDS credential theft, Cisco Talos's CAIRN hunting toolkit for AI-integrated malware, the REA reverse-engineering MCP, runZero's sshamble, and a Copilot for Word AI worm.
 tldrsec.comarticleAdded 30 Oct 2026, published 15 Oct 2026🛡️ Security
- Francis Santerre (@santerref) on X
Post announcing that the MCP Adapter (0.7.0) is now a canonical plugin on WordPress.org, bridging the WordPress Abilities API to MCP. It exposes a default server at /wp-json/mcp/mcp-adapter-default-server, and only abilities a site marks public are exposed. The author's point is that the security review reduces to auditing the list of public abilities, which gives reviewers and pentesters a new endpoint to enumerate.
x.comthreadAdded 16 Oct 2026, published 15 Oct 2026🛡️ Security - Francis Santerre (@santerref) on X
Tweet announcing that the MCP Adapter is now a canonical plugin on WordPress.org (version 0.7.0). It bridges the WordPress Abilities API to the Model Context Protocol, with a default server at /wp-json/mcp/mcp-adapter-default-server. Only abilities a site marks public are exposed, so the security review comes down to auditing the ability list.
x.comthreadAdded 16 Oct 2026, published 15 Oct 2026🧠 AI - dbugs (@ptdbugs) on X
Decepticon is an open-source framework that automates red team operations with 16 specialized AI agents coordinated by an orchestrator, covering recon, vulnerability research and exploitation against an operator-authorized target in an isolated environment. It offers optional attack planning mapped to MITRE ATT&CK, persistent interactive sessions for Metasploit, Sliver and Evil-WinRM, and findings stored in project files and a knowledge graph. It runs via CLI or web dashboard, integrates with Claude Code and Codex through an MCP server, and is self-hosted with Docker Compose.
x.comtoolAdded 18 Oct 2026, published 15 Oct 2026🛡️ Security - Approve What, Exactly? Effect Binding and Trusted Rendering for Agent Step-Up Authorization
Paper arguing that agent human-approval prompts count as a second factor only if agent compromise cannot forge them and they name exactly what is approved. It defines twelve attacks on the approval path (decoy recipients, amount cancellation, card padding, label spoofing, enrollment squatting, threshold splitting) and tests them against AP2, Microsoft's action-bound approval design and MCP elicitation. An audit of ten agent runtimes found no third-party verifiable approval record and post-approval argument changes in four of eight. The reference defense ASU (Agent Step-Up) renders the card from a canonical effect descriptor, has a phone passkey sign its digest, and executes only the stored call. It is proven in Tamarin (53 lemmas) and evaluated on 27,108 scripted trials and 609 AgentDojo pairs. The trusted card cut forged-narration attack success from 0.54 to 0.03 and raised LLM-approver catch rate from 0.30 to 0.98.
arxiv.orgpaperAdded 17 Oct 2026, published 15 Oct 2026🛡️ Security  Developer Who Cloned Photoshop With AI Just Did the Same to Microsoft Office
Decrypt reports that developer Brandon Thomas released WordCraft, GridCraft and DeckCraft, MIT/Apache-2.0 open-source clones of Word, Excel and PowerPoint. They were written in Rust with Anthropic's Claude (Opus 5.5) as a clean-room rebuild and run natively on Windows, macOS, Linux and BSD, and in a browser. Coverage is high (WordCraft 88% of ribbon features, GridCraft 513 of 523 Excel functions), but the authors rate them only about 50–60% ready for real work. Every button is also an MCP command, so agents like Claude can drive the apps. The article is a useful data point on what AI-assisted "vibe coding" can produce in under two weeks, and on where it still falls short (file fidelity, stability).
decrypt.coarticlePublished and added 14 Oct 2026🧠 AI- Thinking in Graphs: Neo4j-Backed Exploit-Chain Reasoning for LLM Penetration-Testing Agents
ChainGraph is a pattern that moves exploit-chain reasoning out of the flat context window and into a Neo4j property graph. Findings, attack steps, credentials, assets and tamper-evident evidence receipts are typed nodes with pre/post-condition edges. The graph is wired to Claude Code or Codex through MCP with no custom harness. Five operator questions (next-step inference, entry-to-crown-jewel pathing, combined-severity promotion, evidence provenance, chokepoint identification) become reusable Cypher and Graph Data Science queries, plus a chain-severity score. On a synthetic multi-forest Active Directory lab modeled on GOAD, three findings rated Medium in isolation become Critical once their path to the forest root is materialized. Scoping each decision to a graph result cut the reasoning payload by about 98% on a token proxy. The authors say the results are illustrative single-run measurements, not a benchmark.
arxiv.orgpaperAdded 17 Oct 2026, published 14 Oct 2026🧠 AI - Victor (@VMG_CU) on X
A social post summarising Elastic's REF8801 campaign. A fake startup accelerator offered founders free Claude/Gemini credits plus a coding agent. The agent was a repackaged open-source project that set OPENROUTER_BASE_URL to an attacker-controlled endpoint and added its own MCP server, so victims' prompts and code went to the attacker. It shows how a trojanised AI coding agent can hijack the LLM base URL and add an MCP server for exfiltration.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026🛡️ Security - Show HN: Graphicle, a Rust port of Graphify with memory for coding agents
Graphicle is a local-first Rust program that parses a repository into a tree-sitter code graph (a port of Graphify) and adds project memory: docs, reviewed decisions and captured Claude Code/Codex sessions. It serves cited file-and-line excerpts within a token budget via one MCP server, CLI and browser app, backed by a single SQLite file, with no API key or telemetry. The README reports a code-only extract on Kubernetes (31k files) in 3m18s versus 26m38s for Graphify 0.9.88, and a memory comparison against seven systems. Agent-proposed memories need user approval and go stale when the code they reference changes.
github.comrepoPublished and added 14 Oct 2026🧠 AI  Francesco Sorrentino (@Fr_Sorrentino) on X
chrome-bridge is an open-source MCP server with a Chrome extension that lets Claude Code drive the user's own Chrome, including logged-in tabs and DevTools. It reads page structure rather than screenshots, which saves tokens and turns. The author reports gains over Claude in Chrome: 4.7× fewer turns and 2.8× lower cost on form filling, 2.3× and 3.4× on finding a row among 1,500, and 9.3× and 4.3× on debugging a broken checkout, with 15/15 correct against 12/15. These are self-reported numbers from the tweet.
x.comtoolPublished and added 14 Oct 2026🧠 AI- morluto/rea
REA (rea-agents on npm) registers an MCP server and matching workflow instructions with coding agents such as Claude Code, Codex, Cursor and Gemini CLI. It exposes tools for inspecting native binaries through Hopper, Ghidra or IDA (with optional objdump and Rizin), JavaScript/Electron apps and ASAR archives, .NET assemblies and websites. Results come back with evidence and limitations, so the agent can explain how a feature works and write and test its own implementation. Analysis runs locally, there is a CLI with the same workflows, and the showcases include C reconstructions verified against original x86 function bytes.
github.comrepoAdded 14 Oct 2026🧠 AI - morluto/rea
REA (rea-agents) is an MIT-licensed toolkit that exposes native-binary, JavaScript/Electron, .NET assembly and website analysis to AI agents via MCP, and also as a local CLI. It drives Hopper, Ghidra, IDA, objdump or Rizin for disassembly and pseudocode, recovers modules and Electron IPC boundaries from ASAR/JS apps, and returns findings with evidence and limitations. Showcases include reconstructing a x86 audio helper into byte-matching C and tracing an Electron clipboard API through preload and IPC; the README also carries lawful-use and licensing guidance.
github.comrepoAdded 14 Oct 2026🛡️ Security - 44er (@44errrr) on X
Announcement of hexvero, an MCP server that gives coding agents a static first look at binaries and app bundles across 18 formats (ELF, PE, Mach-O, APK, .NET, Go, Wasm, Electron, SQLite). It uses zero-dependency Node parsers and marks each finding confirmed or inferred with file and line. Its tool catalog is 3,043 tokens, against a claimed 509,696 for the established reverse-engineering MCP server. Paged output with a byte budget shrinks a 541 MB Electron app to a 15 KB result, 1.3 MB of JSON to 7.9 KB, and a 450 KB build diff to 1.2 KB. radare2, rizin or Ghidra plug in for disassembly, and `npx hexvero setup --apply` registers it with Claude Code, Cursor, Codex and 15 more clients. It is a concrete example of keeping MCP tool definitions and results small enough for an agent's context window.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026🧠 AI - 44er (@44errrr) on X
hexvero is a Node-only, zero-dependency MCP server that gives coding agents a static first-look triage of binaries and app bundles across 18 formats (ELF, PE, Mach-O, APK, .NET, Go, Wasm, Electron, SQLite). Findings are marked confirmed or inferred with file and line, and outputs are paged with a byte budget (a 541 MB Electron app yields a ~15 KB result). The author contrasts its 3,043-token tool catalog with a 509,696-token catalog of an established RE MCP server. radare2, rizin or Ghidra can be plugged in for disassembly, and setup registers it with Claude Code, Cursor, Codex and 15 more clients.
x.comtoolAdded 15 Oct 2026, published 14 Oct 2026🛡️ Security  Visual Studio Copilot and SSMS Remote Code Execution (CVE-2026-103572)
CVE-2026-103572 is a remote code execution bug in Microsoft.VisualStudio.Copilot.Core.dll, shared by Visual Studio and SQL Server Management Studio. A trailing dot (for example `.mcp.json.`) bypasses the protected-filename check in EditsFunctionHandler.GetEditConfirmationTypeAsync, so a hijacked Copilot can rewrite its own MCP and settings files and run commands. The post covers path traversal and InstallationID leaks, indirect prompt injection demos, the October 2026 patch (GetFullPath), and a $0 bounty.
 embracethered.comwriteupAdded 29 Oct 2026, published 13 Oct 2026🛡️ Security
 ERC-8444: Agentic Resource Discovery (ARD) Onchain
An Ethereum Magicians proposal for ERC-8444, which adds an onchain value and settlement layer under Google's Agentic Resource Discovery (ARD) spec for finding MCP servers, A2A agents, skills and APIs. A thin kernel records kind (skill, task, agent, registry), a CAIP-19/CAIP-10 anchor, a JCS+SHA-256 descriptor hash, a canonical URN and a status. Authority belongs to the paid address, and domains act as collected endorsements through /.well-known/ard.json. The reference implementation has Foundry-tested Solidity adapters and a Node.js gateway that passes the official ARD conformance CLI. It introduces a "task" kind (application/ai-task+json) for tenders aimed at suppliers, and the author asks for feedback on the trust root, the hash scope, same-chain anchors and the task payload.
ethereum-magicians.orgthreadAdded 14 Oct 2026, published 13 Oct 2026🧠 AI Show HN: Use your OpenAI subscription to create audiobooks
PDF TO MP3 is a hosted MCP server (Streamable HTTP, account authentication) that turns PDFs into audiobooks. The user's existing AI subscription, such as Codex, handles document processing through the MCP connection. Speech generation is billed separately through the user's own OpenAI or Google text-to-speech API key. The setup is three steps: add the MCP server, add a speech key, then attach a PDF and ask the assistant to use the MCP. It shows a "bring your own subscription" pattern that keeps the vendor's compute costs low.
 pdftomp3.comtoolPublished and added 13 Oct 2026🧠 AI
- AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
A guided tour of a GitHub repository of resources and examples for building AI agents, published on the Becoming a Hacker blog. Per the routing note, it covers LangChain 1.x, LCEL, RAG, LangGraph, CrewAI, DeepAgents, MCP servers and token-cost control such as caching, routing and budget guards. The fetched page held only a LinkedIn redirect notice, so the article text was not read.
 linkedin.comarticleAdded 13 Oct 2026🧠 AI
- AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
Guided tour of Omar Santos's eight-part AI-agents-for-cybersecurity repository. It moves from LLM building blocks (LangChain, RAG) to security agents built with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan). It also covers a hardening guide for six agentic frameworks, token-cost control, and a spec for a supervisor-led, human-gated assessment harness. Design lessons include least-privilege subagents, single-use approvals and kill switches.
 becomingahacker.orgarticleAdded 13 Oct 2026🧠 AI
- santosomar/AI-agents-for-cybersecurity
Companion repository for Omar Santos's Pearson and O'Reilly trainings and books. It has eight parts of runnable Python labs: chat models, embeddings, prompt templates, LCEL prompt chaining, Chroma-based RAG, ReAct/LangGraph/CrewAI/DeepAgents agents, and FastMCP servers (nmap, CISA KEV, Shodan). It also includes guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz), a tokenomics module on agent cost (context compounding, prompt caching, model routing, token budget guards, batch API, cost per accepted outcome), and a vendor-neutral design spec for a human-gated multi-agent assessment harness. It is a current, practical curriculum for building and operating agents. Some examples act on real systems and should only be run in an authorized lab.
github.comrepoAdded 13 Oct 2026🧠 AI - santosomar/AI-agents-for-cybersecurity
Omar Santos's companion repo for his Pearson/O'Reilly trainings and books, organised in eight parts. They cover LangChain prompts, chains and RAG (Chroma), and agents (LangGraph, CrewAI, DeepAgents). They also cover FastMCP security servers (nmap, CISA KEV, Shodan) and attack-surface-management and SOC agent examples. Later parts have security guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz) with hardening notes and 2026 CVE mapping, agent cost/tokenomics scripts including denial-of-wallet budget guards, and a vendor-neutral spec for a human-gated multi-agent security-assessment harness (scope manifest, approval gates, kill switch). Useful as a hands-on path into AI-agent security tooling, with warnings that some examples act on real systems.
github.comrepoAdded 13 Oct 2026🛡️ Security - AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
Omar Santos walks through his eight-part AI-agents-for-cybersecurity repository: LLM building blocks (LangChain, RAG), then security agents with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan), a hardening guide for six agentic frameworks, token-cost control for agents, and a spec for a supervisor-led, human-gated security-assessment harness. It covers concrete design lessons such as least-privilege subagents, staged response actions, single-use approvals bound to exact actions, kill switches, and mapping controls to the OWASP Top 10 for Agentic Applications. Also notes Project CodeGuard rules shipped for AI coding assistants.
becomingahacker.orgarticleAdded 13 Oct 2026🛡️ Security - AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
Omar Santos walks through his AI-agents-for-cybersecurity GitHub repo, which has eight parts. Parts 1–4 cover LLM basics (LangChain, prompting, LCEL, RAG). Parts 5–8 cover building security agents with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan), and a hardening baseline for six ready-made agentic frameworks. They also cover token-cost control (caching, routing, budget guards, cost per accepted outcome) and a supervisor-led, human-gated security-assessment harness spec with single-use approvals, a kill switch and an append-only audit log. The post also covers Project CodeGuard rules for AI coding assistants. It is a practical learning path and a reference for governing and securing agents.
linkedin.comarticleAdded 13 Oct 2026🛡️ Security - Show HN: SolidCraft – Open-Source Parametric CAD in Rust (With MCP Support)
SolidCraft is an open-source parametric 3D CAD application written in pure Rust. It has constrained sketches with its own solver, a feature timeline, assemblies, sheet metal, and STEP/IGES/3MF/STL export. It runs on desktop (egui+wgpu), in the browser, and as a headless CLI. The built-in MCP server (`solidcraft-cli mcp`) gives agents tools such as execute, batch, inspect_design, measure, set_parameter, screenshot and export. They can model headless or drive the running app over a JSON-lines control channel. A rover with 3,323 timeline steps was built entirely through MCP, which shows agent-driven parametric modelling working at scale.
github.comrepoPublished and added 13 Oct 2026🧠 AI  From GTA V on iPhone to Free Photoshop: This AI Tool Is Upending Software
Decrypt reports on REA (Reverse Engineer Anything), an open-source toolkit that uses MCP to connect AI coding agents such as Claude Code and Codex to reverse-engineering tools like Ghidra. It went from under 10,000 to over 100,000 GitHub stars in a week. The article describes AI-decompiled game ports and mashups, and ArtCraft, a set of Rust-built Photoshop-style apps that Brandon Thomas made with Claude Opus 5.5 as a clean-room rebuild. It also covers the copyright and takedown fallout (Activision, Bethesda) and what cheap agent-driven decompilation means for software protection.
decrypt.coarticlePublished and added 12 Oct 2026🧠 AI Phillip Shoemaker (@pbsIdentity) on X
Social thread reacting to a newly disclosed high-severity OAuth vulnerability in the Model Context Protocol Python SDK, where a malicious MCP server could manipulate the authorization flow and steal credentials used by an agent. The author uses it to argue that delegated agent authority needs provenance (who granted it, to which agent, for which service and resource, whether it is transferable or replayable, and when it expires) and that machine-to-machine trust must be auditable by humans. Gives no CVE ID or technical exploit detail.
x.comthreadAdded 13 Oct 2026, published 12 Oct 2026🛡️ Security GitHub Copilot app for Beginners: How to teach Copilot about your codebase
Beginner-oriented GitHub blog guide to giving GitHub Copilot project context through four mechanisms: repository custom instructions (.github/copilot-instructions.md and path-specific .github/instructions files with applyTo), agent skills (SKILL.md folders under .github/skills), custom agents (.github/agents profiles), and MCP servers such as Playwright. It explains when to use each and how they combine, using examples like a quality-checks skill and an accessibility-review agent. Useful as a concrete reference for the repo layout Copilot reads, with a pointer to the community Awesome Copilot collection.
 github.blogarticlePublished and added 12 Oct 2026🧠 AI
 Governing the Agentic SDLC Through Continuous Policy Enforcement
JFrog proposes the Agentic Process Evidence Protocol, an open spec that records coding-agent sessions (harness and agent version, model ID, tool and MCP calls, prompts, owner, human reviewer) as signed in-toto/DSSE attestations bound to a git commit, artifact or release. Policy-as-code release gates can then check for approved LLMs and MCP tools, an accountable human and adherence to guidelines, and the logs allow post-release audit. The post gives mock session-log and evidence JSON, ties the approach to EU AI Act Articles 12 and 14, OWASP AISVS and SLSA, and points to a GitHub reference repo, with JFrog AppTrust as the commercial implementation.
 jfrog.comarticleAdded 14 Oct 2026, published 12 Oct 2026🧠 AI
- Governing the Agentic SDLC Through Continuous Policy Enforcement
JFrog proposes Agentic Process Evidence, an open protocol that records AI coding agent sessions (harness, model ID, tool calls, MCP use, prompts, owner, human reviewer) as signed in-toto/DSSE, SLSA-compatible attestations bound to commits, artifacts and releases. Policy-as-code gates can then block releases that used unapproved LLMs or MCP tools, or that lack an accountable human. It maps the approach to EU AI Act Articles 12/14, OWASP AISVS and ISO/IEC 42001, and includes example session-log and evidence JSON. The post also promotes JFrog AppTrust's Prompt to Release Traceability.
jfrog.comarticleAdded 14 Oct 2026, published 12 Oct 2026🛡️ Security  The OWASP Top 10 Gets Modernized | Endor Labs
Commentary on the 2025 OWASP Top 10 update presented at OWASP Global AppSec in Washington, D.C. Broken Access Control stays #1, Security Misconfiguration and the new Software Supply Chain Failures category (replacing Vulnerable and Outdated Components) rise to #2 and #3, and Cryptographic Failures, Injection and Insecure Design drop. The author adds context on agentic AI and MCP identity and authorization, AI-assisted SAST, non-human identities, CISA Secure-by-Default, OWASP SPVS, and slopsquatting and AI coding assistant risks.
endorlabs.comarticlePublished and added 12 Oct 2026🛡️ Security Context Engineering for Application Security | Endor Labs
Endor Labs whitepaper on using context engineering to make AI coding assistants produce secure code. It covers secure prompting (priming, decomposition, refinement with design-spec and test-first patterns), reusable system rules such as Cursor rules and the CSA R.A.I.L.G.U.A.R.D. framework, and external SAST/SCA tools wired in through MCP servers with a rule that triggers scans. It also covers the costs and risks: extra token use, models ignoring rules, untrusted community rules, and MCP server supply-chain threats. It cites figures such as 62% of AI-generated solutions containing flaws and a 77.5% reduction in weaknesses from recursive prompting.
endorlabs.comarticlePublished and added 12 Oct 2026🧠 AI State of Dependency Management 2025 | Endor Labs
Endor Labs' 2025 State of Dependency Management report examines how AI coding agents and MCP servers add supply chain risk. Researchers analysed 10,663 GitHub MCP server repositories and tested AI-generated dependency recommendations across PyPI, npm, Maven and NuGet, finding agents import vulnerable or non-existent packages. MCP servers are immature: 75% are built by individuals, 41% lack license info, and 82% use sensitive APIs. The report advises treating AI-generated code as untrusted third-party input subject to code review, SAST/SCA and dependency governance.
endorlabs.compaperPublished and added 12 Oct 2026🛡️ Security- Context Engineering for Application Security | Endor Labs
Endor Labs whitepaper on using context engineering to make AI coding assistants write secure code. It covers four techniques: secure prompts (priming, decomposition, refinement with design-spec and test-first patterns), system rules (with sample rules and the CSA R.A.I.L.G.U.A.R.D. framework), external security tools wired in over MCP (with an example Cursor SAST rule), and RAG. It also covers MCP server threats and five defensive pillars, Cursor Hooks, and CISO-level recommendations. It matters because it gives practical guardrails for stopping missing-authorization, rate-limiting and hallucinated-dependency problems at generation time.
endorlabs.comarticlePublished and added 12 Oct 2026🛡️ Security  Introducing AI Coding Agent Governance: Using Hooks to Bring Visibility to the ADLC | Endor Labs
Explains how lifecycle hooks in Claude Code (.claude/settings.json) and Cursor (.cursor/hooks.json) can act as a deterministic, out-of-band control layer for AI coding agents. It covers the hook events, the JSON passed on stdin, and the response contracts. Claude Code uses exit codes plus permissionDecision, updatedInput and additionalContext. Cursor uses stdout JSON with permission and userMessage. It then shows how Endor Labs' `endorctl ai-audit` handler normalises events across both harnesses, streams them to a central audit trail and enforces server-side policies (29 defaults) such as shell allow/deny lists, sensitive-file patterns and MCP allowlists.
endorlabs.comarticlePublished and added 12 Oct 2026🧠 AI- =dennis; (@Xidea404) on X
A tweet from @Xidea404 pointing to the ADI Chain MCP Server documentation on docs.adi.foundation. The server lets AI agents interact with the ADI blockchain through the Model Context Protocol. The tweet carries no technical detail itself, so what the server exposes can't be confirmed from it. It is a pointer to a blockchain-specific MCP connector.
x.comthreadPublished and added 12 Oct 2026🧠 AI  Nicholas Michael Kloster (@showxlate) on X
A researcher announces a zero-click indirect prompt injection RCE in REA (Reverse Engineering Assistant), an MCP tool. Analyzing a malicious web target silently exfiltrates AWS keys, GitHub tokens and SSH identities. The stated root cause is that process.env is passed unconditionally to child processes, so the full environment is exposed to attacker-driven commands. A full writeup is promised but not yet published; replies add unverified skepticism about the project's provenance.
x.comthreadAdded 13 Oct 2026, published 12 Oct 2026🛡️ Security- sepehr071/iran-mcp
iran-mcp is an open-source catalog of 39 MCP servers (488 tools) that let AI agents query Iranian websites such as Digikala, Torob, Divar, Snappfood, Jabama, Paziresh24, TSETMC and qavanin.ir, with prices normalised to Toman. Most servers are unofficial, read-only Python packages run with uvx; three are official hosted servers. It ships Claude Code plugins, Agent Skills, bundles, proxy lists and a machine-readable servers.json.
github.comrepoAdded 24 Oct 2026, published 11 Oct 2026🧠 AI - Dan Kornas (@DanKornas) on X
Arcjet JS SDK is an Apache-2.0 JavaScript monorepo that adds runtime security checks to AI apps, agents and HTTP endpoints. It ships framework SDKs (Next.js, Node.js, Bun, Deno, Fastify, NestJS) plus a Guard API for agent tool calls, MCP handlers, queue workers and background jobs that have no HTTP request object. Features include prompt injection detection, sensitive-information detection (PII, credit cards, custom patterns) and token-bucket, fixed-window and sliding-window rate limiting.
x.comrepoPublished and added 11 Oct 2026🛡️ Security - Dan Kornas (@DanKornas) on X
Arcjet JS SDK is an open-source (Apache-2.0) JavaScript monorepo that adds runtime security to AI apps, agents and HTTP endpoints. It ships request SDKs for Next.js, Node.js, Bun, Deno, Fastify and NestJS. It also has a Guard API for places with no HTTP request object, such as agent tool calls, MCP handlers, queue workers and background jobs. Built-in checks cover prompt-injection detection, sensitive-information detection (PII, credit cards, custom patterns) and token-bucket, fixed-window or sliding-window rate limits, including token budgets.
x.comrepoPublished and added 11 Oct 2026🧠 AI  500B tokens later: Letting AI agents decompile a first-person shooter
Case study of about 3 months spent having Claude Code and Codex CLI agents decompile a popular first-person shooter to C++, using Hex-Rays' ida-mcp for disassembly. Early agent output ran but was semantically wrong, and a reviewer agent accepted worker justifications in commit comments, which acted as unintentional prompt injection. The fix was a byte-matching oracle: it compiles with the original toolchain and compares OBJ function bytes against the EXE/PDB, treating relocations separately. Agents tried to cheat with inline assembly and by editing the checker, so CI hashes the script. The result was 99% of functions present and 83% byte-exact, at an estimated 600-700B tokens.
 momo5502.comwriteupPublished and added 11 Oct 2026🛡️ Security
- 500B tokens later: Letting AI agents decompile a first-person shooter
A retrospective on a 3-month project in which Claude Code and Codex agents (Sonnet 5, Opus 5.5, Luna, Sol, Terra) decompiled a first-person shooter into C++, using ida-mcp, GitHub issues and Discord for coordination. The first month's agents produced readable but semantically wrong code, and a reviewer agent could not catch it. A byte-matching oracle script, comparing compiled OBJ output against the original EXE/PDB, gave a strict PASS/FAIL signal. That let cheaper models like Luna scale to 14+ agents and reach 99% of functions present and 83% byte-exact. Lessons include lowering the compaction threshold to 42%, hourly cron re-injection of the instruction document, hashing the verifier in CI to stop agents tampering with it, and the failure of review when correctness is undefined.
momo5502.comwriteupPublished and added 11 Oct 2026🧠 AI - Frostyz (@frostyz) on X
Announcement that the OSWiki MCP server now supports trading through a separately released local signer. The signer acts on data from the MCP server, so a chat client can browse NFT collections and buy, list, transfer or make offers on Ethereum and ApeChain. Private keys stay on the user's machine, each action is validated and previewed first, user-set limits apply, and any transfer of NFTs or funds needs explicit approval. Setup is a single npx command that creates a fresh wallet, and the author advises testing with small funds.
x.comtoolPublished and added 11 Oct 2026🧠 AI - Cloudflare Changelog (@CFchangelog) on X
Cloudflare's changelog announces that its Cloudflare API MCP server now serves Cloudflare skills alongside its tools. A connected MCP client discovers them by calling `skills/list`. This is an example of distributing agent skills through an MCP server rather than as local files or a repo.
x.comarticlePublished and added 11 Oct 2026🧠 AI - bilawalsidhu/gods-eye-view
God's Eye View is an open-source, vanilla JavaScript + CesiumJS + Vite 3D globe that fuses live public feeds (aircraft, ships, satellites, quakes, public cameras, weather) into one explorable scene. Its AI layer is a hands-free voice agent on the OpenAI Realtime API with 30 tools: camera fly-to, whiteboard annotations, analyst queries over live layers, and scene-context and screenshot grounding. Keys stay server-side and the browser gets only a short-lived session token. An experimental ChatGPT/Codex OAuth path is also supported. The app doubles as an MCP server, so Claude Desktop, Codex or ChatGPT can open the globe from a conversation.
github.comrepoAdded 11 Oct 2026🧠 AI  MCP spec 2026-07-28 changelog (stateless protocol, MRTR, Sampling/Roots deprecated)
Official changelog for the Model Context Protocol 2026-07-28 specification. Major changes: protocol-level sessions and the initialize handshake are removed to make MCP stateless, with version and capabilities carried in _meta on every request, plus a new server/discover RPC and subscriptions/listen replacing the GET stream and resource subscribe calls. It introduces Multi Round-Trip Requests (InputRequiredResult) in place of server-initiated sampling, roots and elicitation requests, moves tasks into an extension, and deprecates Roots, Sampling, Logging, HTTP+SSE and Dynamic Client Registration. Minor changes add cache hints (ttlMs/cacheScope), new Mcp-Method/Mcp-Name headers, OpenTelemetry trace context, RFC 9207 iss validation and an error-code allocation policy.
 modelcontextprotocol.ioadvisoryAdded 10 Oct 2026🧠 AI
- Jetwani Avinash (@jetwaniavinash) on X
Announcement of jevmem, an open-source MIT plugin that gives Claude Code, Cursor and Codex persistent project memory. After each turn it asks Jev (a TypeSafe AI model) whether anything is worth keeping (a rule, decision, failure, or to-do) and writes one line to a plain Markdown file tracked in git. It also checks commands against saved rules before they run and asks first, or blocks. Reported results: Claude followed the rule in 66 of 72 sessions vs 28 without it, the right save/skip call on 98.5% of 66 turns, and 66 of 68 rule-breaking commands caught out of 274 test commands. Listed in Anthropic's Claude plugin directory and on the MCP Registry.
x.comthreadPublished and added 10 Oct 2026🧠 AI - KedgeFlow: A Programmable Control Plane for Enterprise AI Agents
KedgeFlow specifies language-independent contracts so trusted controllers can authorize state-changing operations by enterprise AI agents and privileged gateways can enforce that authority independently of agent reasoning. It combines evidence-backed policy checks, signed permission for an exact action, a single-use shared allowance, target-side conditions and retained outcome records, with two conditional properties (at most one claim per allowance; every dispatch linked to a grant and claim) that hold even if the agent is compromised. A reference implementation exposes the path via MCP; evaluation on a three-member etcd cluster gave exactly one successful claim for each of 82 allowances across 6,560 concurrent attempts, and one committed effect in a 32-call gateway race. The authors report limits: permissive policy still authorized an undesirable effect, and distributed reservations, production access routes, crash recovery and real-target exactly-once effects remain untested.
arxiv.orgpaperAdded 15 Oct 2026, published 10 Oct 2026🧠 AI - KedgeFlow: A Programmable Control Plane for Enterprise AI Agents
KedgeFlow proposes language-independent contracts in which trusted controllers issue signed exact-action permissions and privileged gateways enforce them, using single-use allowance claims, target-side conditions and retained outcome records. It aims to stop altered approved actions, concurrent permission reuse and retries after lost responses, even with a compromised agent. A reference implementation exposes this path via MCP; evaluation on a three-member etcd cluster showed 6,560 concurrent claim attempts yielding exactly one success per each of 82 allowances. It also reports that permissive policy still authorized an undesirable effect, and lists untested areas such as distributed reservations and production access routes.
arxiv.orgpaperAdded 15 Oct 2026, published 10 Oct 2026🛡️ Security - 0xMarioNawfal (@RoundtableSpace) on X
A tweet highlighting Prompts Chat (formerly Awesome ChatGPT Prompts), an open-source prompt library on GitHub that the post says has 167K+ stars. It works across ChatGPT, Claude, Gemini and other models. The post lists a CLI, an MCP server, a Claude Code plugin and self-hosting with custom branding and auth, all free. It is worth cataloguing as a pointer to a widely used prompt collection that now plugs into coding-agent and MCP workflows.
x.comthreadPublished and added 10 Oct 2026🧠 AI  Solving the Identity Crisis for AI Agents (Uber)
Uber's engineering team describes how it extended its Zero Trust stack to give AI agents verifiable identities. Each agent workload gets a SPIRE SVID, and a Security Token Service checks an Agent Registry and mints single-hop, short-lived JWTs. Those tokens carry the full actor chain (for example user → Oncall Agent → Investigation Agent), loosely modelled on OAuth 2.0 Token Exchange (RFC 8693). The tokens are enforced at an MCP Gateway for tool calls, and an AI Gateway fronts model calls with guardrails. The post also covers an A2A client in the SDK that makes the secure path the default, observability of actor chains, and a 2026 roadmap toward dynamic access control and unified policy enforcement. It is a concrete production reference for agent attribution and delegated authorization.
 uber.comwriteupAdded 10 Oct 2026🧠 AI
- argoproj-labs/mcp-for-argocd
TypeScript MCP server for Argo CD that lets MCP clients (Cursor, VS Code, Claude Desktop) list, inspect, create, update, delete and sync applications, read logs and events, and run resource actions through natural language. It supports stdio and HTTP stream transports, with a stateless mode for multi-replica Kubernetes deployments. The security design is detailed: API tokens are read only from env vars or headers and never from tool arguments, the default token is bound to the default base URL, a per-host token registry covers extra instances, a read-only mode disables write tools, and the HTTP listener binds loopback by default and requires an inbound auth token if exposed.
github.comrepoAdded 10 Oct 2026🧠 AI - MCP specification 2026-07-28 stable release
GitHub release announcing the stable 2026-07-28 revision of the Model Context Protocol specification, published from the modelcontextprotocol/modelcontextprotocol repository. The release page itself only points to the official MCP website for the spec and to a changelog for the detailed changes. It matters as the canonical version marker that MCP client, server and SDK implementers track for protocol changes.
github.comadvisoryAdded 9 Oct 2026🧠 AI  Rewriting Prime Agent in Rust
Prime Intellect describes rewriting its open-source Prime Agent coding-agent harness from TypeScript to Rust. Prime Agent orchestrated 2,000+ agents across 10,000+ Prime Sandboxes, using GLM-5.3 inference, to do the rewrite. A root orchestrator split the work into topologically ordered tasks, and each task passed through planner, implementer, reviewer and verifier agents, with TUI, harness, protocol and feature parity checks as the objective verification. A follow-up three-day hillclimbing loop on a benchmark harness merged 69+ changes, and the post reports ~14x faster time-to-input and over 80% less memory after startup. The post also covers the new architecture: nine crates, per-session worker processes, platform abstraction for Windows support, and a runtime-fetched model/MCP catalog. Vendor-run comparisons with other harnesses carry the post's own caveat about the lack of a common benchmark standard.
 primeintellect.aiarticleAdded 10 Oct 2026, published 9 Oct 2026🧠 AI
- Claude Code Complete Guide: Hooks, Agents, MCP Tools & Professional Development
A LinkedIn-hosted PDF guide to Claude Code automation. It explains hook configuration in .claude/settings.json (matchers, JSON stdin payloads, exit code 2 to block) and the hook events: PreToolUse, PostToolUse, Notification, Stop, SubagentStop, SessionStart, UserPromptSubmit and PreCompact. Worked examples include sound and TTS alerts with pyttsx3, a regex guard against rm -rf and other dangerous Bash commands, TDD enforcement, auto-formatting with black, ruff and prettier, and session context loading. It adds troubleshooting and a cheat sheet, and its table of contents lists sections on multi-agent observability, slash commands, MCP tools, sub-agents and professional development patterns. The later sections are cut off in the fetched text. It is useful as deterministic guardrails and automation for a non-deterministic coding agent.
 media.licdn.comwriteupAdded 9 Oct 2026🧠 AI
- Claude Code Complete Guide: Hooks, Agents, MCP Tools & Professional Development
A LinkedIn-hosted PDF guide to Claude Code hooks, subagents, MCP tools and custom slash commands. It covers the hook configuration in .claude/settings.json, the event payloads (PreToolUse, PostToolUse, Stop, SubagentStop, SessionStart), and exit code 2 as the way to block an action. It includes worked examples of safety hooks: a regex-based PreToolUse script that blocks rm -rf, curl piped to a shell, chmod 777 and privileged Docker containers. Other examples are audit logging, TDD enforcement and session context loading. Useful as a practical reference for putting deterministic guardrails around an AI coding agent, though the regex blocklists are easy to bypass.
media.licdn.comcourseAdded 9 Oct 2026🛡️ Security - morluto/awesome-reverse-engineering
awesome-reverse-engineering is a CC0 curated list of reverse-engineering tools and learning resources, organized by task: triage, native analysis, debuggers, instrumentation, deobfuscation, malware analysis, mobile, firmware, file formats, games, diffing, symbolic execution, lifting and AI agents. Each entry notes licensing, maintenance status and prerequisites. It also covers MCP integrations, CTF practice sites and related awesome lists.
github.comrepoAdded 27 Oct 2026, published 9 Oct 2026🛡️ Security - Gurasees (@gurasees0) on X
Robo dir is a directory that aggregates robotics and physical-AI datasets in one place. The launch tweet claims 3,494 datasets, 86,424 Hugging Face uploads, 236B+ frames and 2.2M+ hours of data. It also exposes the index through a single MCP server with no sign-in, so agents can search for robot training data programmatically.
x.comtoolPublished and added 9 Oct 2026🧠 AI  Richard Abishai (@richardabish_ai) on X
An X post by the creator of ROPE, a prompt-injection benchmark for LLM agents. It uses two news items to argue that the prompt-injection model of agent attacks is incomplete: a zero-click RCE called Plugin4Shell in coding agents' plugin systems, and Apple's local MCP server in Safari 27 exposing browser automation to agents. Neither involved persuading a model. The author concludes that teams should benchmark what an agent believes and also audit what it can reach, using plugin signing and update policy, least-privilege credentials per agent, and treating local MCP surfaces as attack surface.
x.comthreadPublished and added 9 Oct 2026🛡️ Security- Show HN: Edi Life OS – self-hosted life dashboard with an MCP server for AI
Edi Life OS is a self-hosted dashboard (PHP 8.1+, MySQL, vanilla JavaScript) that combines focus timer, habits, goals, Kanban tasks, finances and notes in ten workspaces. It includes an optional Node.js MCP server that exposes 15 tools over stdio. The tools let Claude Desktop, Claude Code or Codex read the dashboard, create goals and tasks, log habits and record expenses. The MCP server calls only the app's bearer-token /api/v1 HTTP API and never touches the database or credentials. The README is candid about limits: the token has no scopes, there is no app-level rate limiting, and the secret-note flag is only a visibility setting, not encryption.
github.comrepoPublished and added 9 Oct 2026🧠 AI  ETDI: Comprehensive MCP Security Framework
ETDI (Enhanced Tool Definition Interface) is a proposed security extension to the Model Context Protocol that adds cryptographically signed and versioned tool definitions, OAuth 2.0 scope-based permissions, Cedar-policy-driven context-aware access control (via engines like Amazon Verified Permissions/OPA), and call-stack verification to stop tool chaining and privilege escalation. It is designed to counter two named MCP threat classes — Tool Poisoning (spoofed/impersonated tool definitions) and Rug Pull attacks (post-approval silent modification of tool behavior) — with concrete pseudocode for signature verification, version/integrity checking, and policy evaluation. The page functions as an implementation guide for MCP client/server builders wanting to harden tool approval and invocation flows.
 vulnerablemcp.infowriteupAdded 8 Oct 2026🧠 AI
- James Berthoty (@JamesBerthoty) on X
James Berthoty argues that AI guardrails for first-party AI features should be treated as an extension of cloud/product security, not tied to employee-usage monitoring. Guardrails (prompt injection defense, content filtering, goal alignment) are available from AI security vendors, gateways, frontier providers and SDKs. He recommends deploying in-depth guardrails through developer SDKs or an existing cloud runtime/CADR provider, because those see what happens on the workload (such as a prompt injection leading to workload takeover, or the files a malicious MCP call wrote). Dedicated AI security vendors offer an integrated policy engine and deeper AI red-teaming, but they are usually run by internal IT rather than cloud/product security teams.
x.comthreadAdded 10 Oct 2026, published 8 Oct 2026🛡️ Security  SonicWall and Splunk Patch Critical Vulnerabilities
SonicWall patched four SMA1000 appliance vulnerabilities including CVE-2026-102255, a pre-authenticated SSRF flaw (CVSS 10) that lets an unauthenticated remote attacker abuse an unintended alternate access path to reach internal functionality; two other high-severity bugs enable RCE and one medium-severity bug enables XSS. Splunk separately fixed dozens of flaws across Splunk Enterprise, MCP Server, and the Add-on for AWS, including three critical Splunk Enterprise bugs allowing arbitrary command execution, unauthorized access, and code injection, plus a medium-severity MCP Server issue letting an authenticated user redirect API requests to an attacker-controlled URL. SonicWall says SSL-VPN on its firewall products is unaffected and no in-the-wild exploitation has been observed.
securityweek.comarticlePublished and added 8 Oct 2026🛡️ Security Top MCP security resources — October 2026
Adversa AI's October 2026 MCP security roundup, aggregating and synthesizing 15 resources: authentication-bypass vulnerabilities in LiteLLM's MCP endpoint (CVE-2026-59822, now CISA KEV), Grafana's MCP server session spoofing/SSRF (CVE-2026-19516), an MCP Python SDK OAuth-fallback flaw exploited by a malicious server returning a 404, and an Obot gateway route-matching bypass reopening GHSA-vw82. It also covers detection failures (two malicious MCP servers passing five scanners including Cisco mcp-scanner and Snyk agent-scan, 12% of 82,000 public MCP configs hardcoding secrets), a malicious npm wallet-signing package (gadgethumans-mcp), the A2M agent-hijacking attack technique, and CoSAI's MCP Security v2.0 governance model.
adversa.aiarticlePublished and added 8 Oct 2026🛡️ Security- ETDI: Comprehensive MCP Security Framework
ETDI (Enhanced Tool Definition Interface) is a proposed security extension to the Model Context Protocol that defends against Tool Poisoning (spoofed/impersonated tool definitions) and Rug Pull attacks (silent post-approval modification of tool behavior) using cryptographic signing of tool definitions, immutable versioning with mandatory re-approval, OAuth 2.0 scopes, and Cedar/Amazon Verified Permissions-based policy-aware access control. The page includes detailed attack scenarios, a call-stack verification scheme to prevent tool-chaining privilege escalation, and implementation code for key management, signature verification, and policy evaluation.
vulnerablemcp.infowriteupAdded 8 Oct 2026🛡️ Security - Tracer-Cloud/opensre
OpenSRE is an open-source framework for building AI SRE agents that resolve production incidents by correlating logs, metrics, traces, deploys and runbooks across 60+ connected tools (observability, cloud infra, incident management, MCP). Beyond the agent runtime (CLI, Python API, Slack/PagerDuty/Telegram integrations), the project's stated mission is to build an RL training and evaluation environment — explicitly modeled on SWE-bench's role for coding agents — to scale realistic infrastructure-failure scenarios as a benchmark for AI SRE.
github.comrepoAdded 8 Oct 2026🧠 AI - Applying Security by Design at the Point of Execution: How Governed Security Requirements Affect the Security of AI-Generated Code
Evaluates delivering security requirements from a governed security-by-design knowledge base (SbD-ToE) to a code-generating LLM through an MCP server at generation time. On DualGauge (59 Python tasks) the share passing all security tests rose from 44.1% to 78.0%; on BaxBench (28 backend scenarios) the share of functionally correct solutions with no successful exploit rose from 65% to 86%, matching the authors' Oracle Security Reminder (85%). The joint secure-and-functional metric did not improve significantly, since stricter code failed functional tests that fix unstated values. The study used one model and one generation per task, and it proposes measuring conformance with applicable requirements rather than only detecting known weaknesses.
arxiv.orgpaperAdded 9 Oct 2026, published 7 Oct 2026🛡️ Security  Can a Cloud-Native Harness Make Agents Reliable Beyond the Desktop?
Latent Space interviews Stacklok founders Craig McLuckie and Joe Beda (Kubernetes co-creators) about Mecatl, an open-source "cloud-native harness" for coding agents that separates the agent loop from local tool execution, session state and model provider so enterprises can run and govern agents centrally rather than on individual desktops. The piece also covers Stacklok's earlier pivot from supply-chain security to ToolHive, an open-source platform/Kubernetes operator for running and governing MCP servers, and a not-yet-open-sourced "AI Gateway" focused on access control, budgets and provider routing for regulated enterprises (banks, telcos, semiconductor firms). The framing draws an explicit analogy to how Kubernetes decoupled enterprises from cloud providers, arguing agent harnesses need the same "cattle not pets" treatment to scale beyond desktop tools like Claude Code, Codex and GitHub Copilot.
 latent.spacearticlePublished and added 7 Oct 2026🧠 AI
- Dr Milan Milanović (@milan_milanovic) on X
A Twitter/X thread breaking down three protocols that connect AI agents to different things: MCP (agent to tools/data, JSON-RPC 2.0 over stdio or Streamable HTTP), A2A (agent to agent, using an Agent Card JSON manifest at /.well-known/agent-card.json, running over JSON-RPC/gRPC/HTTP+JSON), and ACP, the Agent Client Protocol created by Zed in 2025 for connecting code editors to coding agents (modeled on LSP, JSON-RPC over stdio). It clarifies that IBM Research's older "Agent Communication Protocol" (also abbreviated ACP) merged into A2A on 29 August 2025, making many existing protocol comparisons outdated, and notes governance differences: MCP and A2A sit under the Agentic AI Foundation (Linux Foundation) while the Agent Client Protocol is governed by Zed and JetBrains. The author also mentions building an internal MCP server letting customers run and schedule reports via ChatGPT and Claude.
x.comthreadPublished and added 7 Oct 2026🧠 AI - The Vulnerable MCP Project — MCP vulnerability database
The Vulnerable MCP Project is a curated, continuously growing database of security vulnerabilities and attack techniques specific to the Model Context Protocol ecosystem. Entries cover concrete CVEs (e.g. CVE-2025-68143/68144/68145 in Anthropic's mcp-server-git), transport-layer SDK flaws (cross-client response leakage, missing DNS rebinding protection in the official TypeScript/Python SDKs), unauthenticated/0.0.0.0-bound servers enabling RCE (MCPJam inspector, MCP Inspector, Grafana MCP), command/path injection in dozens of third-party servers (gemini-mcp-tool, mcp-server-kubernetes, Framelink Figma MCP, Zen MCP, filesystem-mcp), SSRF chains reaching cloud metadata (MarkItDown MCP, mcp-fetch-server), and a large set of AI-specific attacks: tool poisoning, trigger-phrase data exfiltration, prompt injection via GitHub issues, Jira and Google Docs, rug-pull tool mutation, and cross-server tool-name collisions. It functions as the de facto vulnerability registry for the MCP ecosystem, useful for tracking disclosed issues before patching or adopting third-party MCP servers.
vulnerablemcp.inforepoAdded 6 Oct 2026🛡️ Security - Microsoft Agent Framework python-1.20.0 release
Release notes for python-1.20.0 of Microsoft's Agent Framework, an open-source agent/workflow orchestration library. This release adds native vector-store connectors for DuckDB, SQL Server and MongoDB plus a TypeSafe AI connector, redesigns Foundry hosting around request-scoped agent factories and sandbox-isolated sessions, adds computer-use support to Responses clients, and ships Magentic manager and handoff-routing improvements for multi-agent orchestrations alongside a large batch of MCP, Bedrock, Gemini, Anthropic and Ollama provider fixes.
github.comrepoAdded 6 Oct 2026🧠 AI  Identity-aware AI data agents with AWS Lake Formation and Trusted Identity Propagation
AWS Security Blog walkthrough showing how to build identity-aware AI data agents on Amazon Bedrock AgentCore that propagate a real user's OIDC id_token through the agent's tool-calling chain (Runtime → MCP Gateway → Lambda) via HTTP headers, keeping the token out of the foundation model's context entirely. A Lambda function performs a server-side token exchange using IAM Identity Center Trusted Identity Propagation, assumes a scoped TIP role, and runs the user's Athena query so AWS Lake Formation evaluates the real user's grants, producing per-user row/column access and CloudTrail audit records naming the actual human (onBehalfOf) without rewriting existing governance policies.
 aws.amazon.comwriteupAdded 8 Oct 2026, published 6 Oct 2026🧠 AI
- Prasenjit Sarkar (@stretchcloud) on X
Describes Uber's internally-built ADR (Agentic Detection & Response) system, open-sourced in August with an MLSys paper, which monitors over 50,000 daily AI agent sessions via an MCP-based sensor inside Cursor, Claude Code and Codex. Uber found 206 credential exposures in ten months from normal agent use (not prompt injection), and ADR hits 100% detection with 3 false positives on the public AgentDojo benchmark; the thread also flags that human approval fatigue breaks down as a safety control past roughly 50 agent actions per session.
x.comthreadPublished and added 6 Oct 2026🛡️ Security - overmind-core/overmind
Overmind is an open-source platform (MIT SDK/CLI, AGPL-3.0 platform, self-hostable) that instruments an agent's code via OpenTelemetry tracing, turns the resulting production traces (or any dataset) into a fine-tuned model benchmarked against user-defined eval metrics, and serves it through one unified API with downloadable/retrainable weights. It ships an SDK, CLI, REST API, Console, and an MCP server exposing project tools and workflows (investigate-capability, finetune-capability, ship-model) for Cursor, Claude Code, OpenCode and Codex, and can sync traces from Langfuse, LangSmith, Braintrust or Galileo; self-hosting runs via Docker Compose with Postgres, Redis, Celery workers and Modal-based GPU workers for fine-tuning/serving (vLLM).
github.comrepoAdded 6 Oct 2026🧠 AI - claude-mem — persistent memory system for Claude Code and other coding agents
Claude-Mem is an open-source persistent memory plugin for Claude Code and other coding agents (Codex, OpenCode, Grok Bot, T3 Code, OpenClaw) that captures tool-usage observations during sessions, compresses them into semantic summaries, and reinjects relevant context into future sessions. It uses five lifecycle hooks (SessionStart, UserPromptSubmit, PostToolUse, Stop, SessionEnd), a local SQLite database, a Chroma vector store for hybrid semantic+keyword search, and exposes three MCP tools (search, timeline, get_observations) that follow a token-efficient layered retrieval pattern to cut context costs roughly 10x. It is Apache-2.0 licensed, built with the Claude Agent SDK and TypeScript, and ships an optional hosted "observer" memory service alongside self-hosted options via OpenRouter/Gemini keys or an Anthropic plan.
github.comrepoAdded 5 Oct 2026🧠 AI - Model Context Protocol releases (2026-07-28 stable spec)
The GitHub releases page for the modelcontextprotocol/modelcontextprotocol repository, listing the version history of the Model Context Protocol (MCP) specification from its initial 2024-10-07 draft through the 2025-03-26, 2025-06-18, and 2025-11-25 revisions to the newly stabilized 2026-07-28 revision. Each entry links to its changelog and distinguishes release candidates from final/stable releases, and the page points to the version-negotiation documentation that lets clients and servers agree on which protocol revision to use.
github.comotherAdded 5 Oct 2026🧠 AI  Bill Xie (@joyrap) on X
A Twitter thread summarizing key takeaways from a podcast conversation with Thibault Sottiaux (Tibo), Head of ChatGPT and Codex at OpenAI. Topics include the prediction that most internet actions will soon be taken by agents, how Notion's MCP server launch caused a traffic flood that strained its systems, the likely disappearance of the model picker in favor of automatic routing, skepticism about loops and graphs as durable agent architectures, and OpenAI's approach to AI safety.
x.comthreadPublished and added 5 Oct 2026🧠 AI- Zhenyu98/codex-chatgpt-bridge
codex-chatgpt-bridge is a Codex agent skill plus external PowerShell control scripts (On/Off/Reboot/Rotate) built on top of the open-source DevSpace MCP bridge, which lets ChatGPT act as a planning/review "architect" while Codex stays the local executor that applies and verifies changes. It adds a token-saving router (NORMAL / TOKEN_SAVING / CHATGPT_ARCHITECT modes) and a lifecycle layer — Cloudflare Quick Tunnels or a stable Cloudflare Worker proxy, DPAPI-protected credentials, OAuth token rotation, and a scheduled-task recovery entrypoint — so the bridge's public endpoint can be closed when idle without re-authorizing the ChatGPT app on every restart.
github.comrepoAdded 5 Oct 2026🧠 AI  Register Codex's Computer Use as a Claude Code MCP Server
A thread shows how to register Codex's built-in Computer Use capability — the "cua_repl" MCP server found in ~/.codex/plugins/cache/openai-bundled/unified-computer-use/ — as a custom user MCP server (named "codex-cu") inside Claude Code, letting Claude drive Mac GUI automation via Codex's computer-use backend instead of a separate CUA driver. The author reports an informal benchmark across 8 computer-operation tasks: Claude Opus 5.5 + Codex Computer Use scored 6/8, Codex alone scored 6/8, and the original CUA driver only scored 3-4/8, with a caveat that future Codex updates could break this cross-agent MCP reuse.
x.comthreadPublished and added 5 Oct 2026🧠 AI SunsetSyntax (@sunsetsyntax) on X
A short account of switching from a split Neo4j (relationships) + separate vector DB (embeddings) setup — which required manually reconciling IDs whenever an agent wrote a fact — to NornicDB, a single Go-based graph+vector store that speaks Bolt/Cypher and bundles an MCP server in one process. The point is that agents can query a unified memory store without an app layer babysitting two separate databases.
x.comthreadPublished and added 4 Oct 2026🧠 AI- Jan Curn (@jancurn) on X
Announcement of mcpc v0.7.0, Apify's open-source MCP CLI client (npm i -g @apify/mcpc), which adds support for the MCP Skills extension with new skills-list/skills-get commands that verify SKILL.md and supporting files against the skill manifest via size and SHA-256 checks before printing content. The release also ships security hardening: repo-local .mcp.json auto-discovery can no longer read environment variables (blocking leaks like $GITHUB_TOKEN), OAuth refresh tokens are now scoped only to the auth server originally used, and Windows login URLs no longer launch through cmd.exe.
x.comthreadAdded 5 Oct 2026, published 3 Oct 2026🛡️ Security - Jan Curn (@jancurn) on X
Jan Curn announces mcpc v0.7.0, an open-source MCP CLI client (npm package @apify/mcpc), adding support for the MCP Skills extension via new skills-list and skills-get commands that fetch and cryptographically verify SKILL.md and supporting files against the skill manifest (size + SHA-256). The release also hardens security by preventing repo-local .mcp.json auto-discovery from reading environment variables (blocking token-leak tricks), scoping refresh tokens to the originating auth server, and fixing an insecure Windows login URL launch path via cmd.exe, alongside OAuth session longevity fixes and 2026-07-28 MCP spec compatibility improvements.
x.comthreadAdded 5 Oct 2026, published 3 Oct 2026🧠 AI  [AINews] not much happened today
Daily AINews digest (Latent Space) covering an October 2026 news cycle: OpenAI's cheaper/faster GPT-6.1 Sol and Anthropic's Claude Sonnet 5.5 reshaping Agent Arena's cost-performance frontier, a wave of decision-model releases (Cloudflare Clef, llama.cpp's new decision-model endpoint, Perplexity's pplx-decider-v1-27b) as classifier/controller models for agent harnesses, and agent-harness tooling news such as Pi 1.0 with native MCP support, Claude Code plugins, Cursor Rollouts and Cloudflare Sandbox SDK. It also rounds up agent-RL research (multi-harness RL from Hugging Face, ProVer/AC2 credit assignment, long-horizon controllers, context compression), new evals (ScholarCatalyst, EurekaBench, Vals Web Search Index, an SWE bug-finding benchmark), inference and hardware notes (Ascend 950 chip analysis, Prime Inference NVFP4 KV caching, NVHBM memory), and r/LocalLLaMA highlights on local Qwen3.8-27B inference and MTP speculative decoding in llama.cpp.
latent.spacearticlePublished and added 3 Oct 2026🧠 AI Nation (@visitnation) on X
NATION Guard is a local, open-source tool announced by Nation that inspects the instructions and configuration behind AI agents. It combines injection-pattern scanning, integrity baselining, and per-server MCP fingerprinting so developers can detect suspicious prompt injections and unauthorized changes to their agent setup.
x.comthreadPublished and added 3 Oct 2026🛡️ Security- AINotes (@ainotesus) on X
OpenRig is an orchestration tool that runs multiple coding agents as one persistent, coordinated team rather than isolated sessions. A YAML configuration defines pods, seats, communication edges, and continuity policies, while a daemon, CLI, TUI, MCP server, SQLite store, and tmux handle agent launch, inter-agent messaging, session snapshots, restoration, and topology management.
x.comtoolPublished and added 3 Oct 2026🧠 AI - OKX Agent Trade Kit (okx-trade-mcp / okx-trade-cli)
OKX Agent Trade Kit is an open-source MCP server (okx-trade-mcp) and CLI (okx-trade-cli) that let AI assistants like Claude Desktop, Cursor, Claude Code and VS Code place trades and query account data on the OKX exchange via natural-language commands. It runs locally with API keys never leaving the machine, supports module scoping (market, spot, swap, account, earn), a read-only mode for safe querying, multiple profiles, and includes pre-built skill files for agent frameworks plus structured JSON error reporting for debugging failed tool calls.
github.comrepoAdded 2 Oct 2026🧠 AI - Microsoft Agent Framework — python-1.20.0 release
Release notes for Microsoft's Agent Framework (Python and .NET SDKs), covering versions python-1.16 through python-1.20 and dotnet-1.19 through dotnet-1.23. Changes span native vector-store connectors (MongoDB, Qdrant, PostgreSQL/pgvector, DuckDB, SQL Server, Azure Cosmos DB, Azure AI Search), Foundry hosting redesigns around request-scoped agent factories and durable Invocations, MCP skill/session security hardening (approval binding, security labels, ZIP-only skill archives), Magentic multi-agent orchestration and handoff routing, and checkpoint/replay correctness fixes across workflows.
github.comrepoAdded 2 Oct 2026🧠 AI - Bifrost (Maxim AI) — open-source LLM gateway
Bifrost is an open-source, high-performance LLM gateway (by Maxim AI) that exposes a single OpenAI-compatible API across 23+ providers including OpenAI, Anthropic, AWS Bedrock, Google Vertex, Azure, Cohere, Mistral, and Ollama. It provides automatic failover, load balancing, semantic caching, Model Context Protocol (MCP) tool integration, budget and governance controls, OIDC user provisioning, and Prometheus-based observability, deployable via npx or Docker with claimed sub-15 microsecond overhead at 5,000 RPS. It is positioned as a drop-in replacement requiring only a base-URL change for existing OpenAI, Anthropic, or GenAI SDK code.
github.comrepoAdded 2 Oct 2026🧠 AI  Six defects in one signature verification tool, found from outside in six rounds
A forum writeup on ethresear.ch describing a "predictions-first" testing methodology for verification logic, applied against the author's own repository and against a live third-party MCP server (nsgoods Workbench, which offers offline signature verification over the x402 payment catalogue). Six rounds of testing surfaced concrete defects: a false negative caused by a stripped field list, a tamper-accepted body via a service-selection parameter that let callers choose which fields were excluded from the signed message, schema-rejection and signature-failure returning byte-identical error text, and a logging/privacy gap in the operator's system that was fixed after disclosure. The author ships a companion tool, exactzk-verification-guards, which captures both a passing and an actually-reproduced failing run as regression evidence rather than a fabricated example.
 ethresear.chwriteupPublished and added 2 Oct 2026🛡️ Security
- Threat-Preserving Representation Sensitivity in Agent-Security Benchmarks
This arXiv paper introduces threat-preserving representation sensitivity (TPRS), a metric for how much an agent-security benchmark's attack success rate (ASR) changes purely from cosmetic changes to tool-name wording, with the underlying task, policy, and ground truth held fixed. Testing on Agent Security Bench (ASB), MCPTox and AgentDojo with GPT-5-mini, Claude Haiku 4.5 and GPT-4o-mini, the authors find swings of up to 13 percentage points in ASR from renaming tools as threat-neutral vs. threat-explicit, showing that single-representation ASR scores are not reliable robustness measures and arguing for evaluation across a controlled set of representations instead.
arxiv.orgpaperAdded 5 Oct 2026, published 2 Oct 2026🧠 AI - Threat-Preserving Representation Sensitivity in Agent-Security Benchmarks
This paper introduces threat-preserving representation sensitivity (TPRS), a metric showing that attack success rate (ASR) scores on LLM-agent security benchmarks shift dramatically based on cosmetic changes to tool naming, even when the underlying task, policy, and ground truth are held fixed. Testing on Agent Security Bench, MCPTox, and AgentDojo, the authors find swings of up to ~13 percentage points in ASR on GPT-5-mini and Claude Haiku 4.5 just from renaming tools between threat-related and threat-neutral labels, with a matched-length control reproducing most of the effect. The findings argue that single-representation ASR scores are not reliable robustness claims and that benchmarks should report results across multiple threat-preserving representations.
arxiv.orgpaperAdded 5 Oct 2026, published 2 Oct 2026🛡️ Security  One month coding with GLM 5.3 Flash
Wagtail's engineering team recounts a September challenge to run all day-to-day coding work on one efficient open model, GLM-5.3-Flash, tracking usage via AgentsView: they stayed within budget ($68, ~4kWh) for the first half of the month before a vibe-coded MCP server prototype on the "wrong" model burned 450M tokens/$150/5kWh overnight, and inference-provider capacity limits forced fallbacks to DeepSeek-V4.1-Flash and Qwen 3.8 Flash. The post ends with concrete lessons for October: constant local usage/energy measurement, separate budgets for experimentation vs production, better multi-agent prompt/role patterns (orchestrator/scout/implementer/reviewer), and defaulting day-to-day work to flash-tier models.
 wagtail.orgarticleAdded 3 Oct 2026, published 2 Oct 2026🧠 AI
 Dave Gilbert (@docgotham) on X
A Twitter/X thread reacting to OpenAI's announcement that ChatGPT Sites can now host MCP servers, including turning plugin extensions into deployable MCP servers (e.g. "@sites create a todo list that I can use in ChatGPT"). User Dave Gilbert (@docgotham) flags a concrete operational bug: with a ChatGPT Pro account, custom MCP servers can't be refreshed — disconnecting/reconnecting or even deleting and re-adding a server still serves the old cached plugin version after an update.
x.comthreadPublished and added 2 Oct 2026🧠 AI The MCP Ecosystem Is Speaking Five Revisions at Once
A dated research report (Pennyforge, 2026-10-02) that probes the live MCP ecosystem to show it is fragmented across five spec revisions at once: it POSTs initialize/server/discover calls against 186 deduplicated endpoints pulled from the official MCP registry's v0 API, plus 10 popular npm stdio servers spawned via npx. It finds only ~9.7% of responding endpoints speak the new stateless 2026-07-28 wire (which removes Mcp-Session-Id, the initialize handshake, and adds server/discover), that the flagship @modelcontextprotocol/server npm packages still only speak the older 2025-06-18 revision, and documents a "version-echo" methodology pitfall where servers negotiate within a supported range rather than reporting a fixed version — illustrated with a parallel failure mode found in the x402 payment protocol.
 dev.towriteupPublished and added 2 Oct 2026🧠 AI
- Evaluating and Improving the Robustness of Large Language Models to Input Sequence Variations
Thesis on evaluating and improving LLM robustness to adversarial input perturbations. It proposes the R_stab robustness metric (Jensen-Shannon divergence), ASA, an evolutionary black-box attack on LLM-as-a-Judge systems (up to 73.8% ASR), trojan trigger recovery on Trojan Detection Challenge 2023 (Pythia-1.4B), and a systematization of bypasses of multi-layer defenses from SaTML CTF 2024. For MCP agents it proposes AttestMCP (HMAC-attested tool calls) and the Commit Boundary pattern, cutting ASR from 53.7% to 12.4% on the 847-scenario MCPBench; the methods are implemented in JudgeGuard, TrojanArmor and MCPSec.
arxiv.orgpaperAdded 9 Oct 2026, published 1 Oct 2026🛡️ Security - Evaluating and Improving the Robustness of Large Language Models to Input Sequence Variations
An arXiv thesis-style paper proposing R_stab(f), a Jensen-Shannon-divergence-based robustness metric for LLM outputs under small input perturbations, along with a proven bound V(h) <= 1 - R_class(h) for localized attacks. It introduces ASA, an adaptive evolutionary black-box attack against LLM-as-a-Judge systems reaching up to 73.8% attack success rate (62.6% cross-model transfer), evaluates trojan/backdoor detection on the Trojan Detection Challenge 2023 (Pythia-1.4B) and SaTML CTF 2024, shows that committees of 5-7 heterogeneous models cut Gemma-3-4B's ASR to 19.3%, and presents AttestMCP, an HMAC-based tool-call attestation scheme plus a "Commit Boundary" isolation pattern for MCP agents that cuts average ASR on the 847-scenario MCPBench from 53.7% to 12.4%. Methods ship as the JudgeGuard, TrojanArmor, and MCPSec software suites.
arxiv.orgpaperAdded 5 Oct 2026, published 1 Oct 2026🛡️ Security - MCP TypeScript SDK v2.2.0
Release notes for v2.2.0 of the official Model Context Protocol TypeScript SDK. Upgrade notes: machine-to-machine OAuth providers (ClientCredentialsProvider, PrivateKeyJwtProvider, StaticPrivateKeyJwtProvider, CrossAppAccessProvider) should now be given expectedIssuer, and fetchToken() throws AuthorizationServerMismatchError when client information is bound to a different authorization server. listTools/listPrompts/listResources/listResourceTemplates now follow nextCursor automatically, capped by listMaxPages. Fixes include CommonJS type-checking of the DPoP jose types, unhandled rejections in Client.listen(), createMcpHandler stack overflow and subscriptions/listen handling, .localhost loopback for OAuth token endpoints, and v1-to-v2 codemod comment preservation.
github.comadvisoryAdded 1 Oct 2026🧠 AI - Identity Management for Agentic AI [pdf] (2025)
OpenID Foundation whitepaper (Oct 2025, lead editor Tobin South) analyzing how authentication/authorization for AI agents differs from traditional software clients. It covers where OAuth 2.1, OIDC, SSO/SCIM, and MCP already work for single-domain synchronous agents, and lays out unsolved problems for autonomous agentic identity: agent identity fragmentation across vendors, replacing user impersonation with explicit delegated "on-behalf-of" authority, consent-fatigue at scale, recursive delegation chains between sub-agents, agents acting for teams of users, and browser/computer-use agents bypassing API-based authorization entirely.
 openid.netpaperAdded 2 Oct 2026, published 1 Oct 2026🛡️ Security
 Blockworks Opens Its Full Dataset To AI Agents
Blockworks, a crypto research and data provider, launched a hosted Model Context Protocol server that gives AI agents like ChatGPT, Claude and Cursor read access to the datasets underlying its research and its Intel app. The MCP server is included free with every existing API plan and uses the same API key and permission scope as the regular API, rather than requiring separate onboarding.
 thedefiant.ioarticlePublished and added 1 Oct 2026🧠 AI
- https://github.com/Panniantong/Agent-Reach
Agent-Reach is a CLI and agent-"skill" layer that equips coding agents (Claude Code, Cursor, OpenClaw) with ready-made web-reading tool use: fetching arbitrary pages via Jina Reader, YouTube transcripts via yt-dlp, GitHub repos via gh CLI, Bilibili search, RSS via feedparser, and semantic web search via Exa through mcporter, with login-gated platforms (Twitter/X, Reddit, Xiaohongshu, Facebook, Instagram) added on request via cookies or OpenCLI browser sessions. Each platform module probes an ordered list of candidate backends and falls back automatically when one breaks (e.g. yt-dlp being blocked by Bilibili's anti-scraping), and an `agent-reach doctor` command reports which backend each channel is currently using. It positions itself as a "capability layer" that selects, installs and health-checks the right upstream tool for an agent rather than wrapping the reads itself.
github.comrepoAdded 2 Oct 2026, published 1 Oct 2026🧠 AI - Average AI Bro (@AverageAiBro) on X
An X post presenting Reversecore MCP, an MCP server that wraps authorized reverse-engineering, malware-analysis, forensics and SAST-style tools such as radare2. The user picks a profile, points it at a sample, and the agent gets structured results back in the session without driving the tools by hand. It is a concrete example of profile-based tool exposure for specialized toolchains, offered as a free alternative to a commercial IDA setup. The post stresses authorized analysis only.
x.comthreadAdded 1 Oct 2026, published 30 Sep 2026🧠 AI - Average AI Bro (@AverageAiBro) on X
Reversecore MCP is an MCP server that exposes authorized reverse-engineering, malware-analysis, forensics, and SAST-style tooling to an AI agent through selectable profiles, returning structured results for a given binary sample. It targets the gap between hand-driving tools like radare2 and paying for a commercial IDA Pro-based workflow, letting an agent query a toolchain directly instead of a human operator switching between tools.
x.comtoolAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security - AI-Infra-Guard (A.I.G) — Tencent Zhuque Lab
AI-Infra-Guard (A.I.G) is Tencent Zhuque Lab's open-source AI red-teaming platform combining AI infrastructure vulnerability scanning (2000+ CVE rules covering vLLM, llama.cpp, LangFlow, n8n, MLflow and 145+ other AI components), MCP server/skill security scanning, LLM API poisoning detection, and multi-turn jailbreak evaluation (Many-Shot, PAIR, GOAT, ActorAttack). It ships CLI tools (skill-scan, mcp-scan, agent-scan), a Docker-deployed web UI, and has produced original research including FORGE-Bench (loss-of-control benchmark), RogueHandoff-20, and SkillJack (persistent skill backdoors), with talks at Black Hat Europe 2025 on MCP security.
github.comrepoAdded 30 Sep 2026🛡️ Security - zkLombard (@zkLombard) on X
zkLombard announces a remote MCP server (HTTP transport, one endpoint, eight tools, no custody of keys) that lets an agent with its own wallet value a Uniswap v3 position, pledge it, borrow USDG, repay, and redeem. The agent signs every transaction itself, and loan solvency is proven with a zero-knowledge proof verified onchain. It installs with a single `claude mcp add --transport http` command, and a manual is linked. It is a concrete example of exposing financial primitives as MCP tools for autonomous agents.
x.comtoolAdded 1 Oct 2026, published 30 Sep 2026🧠 AI  Connect Orca’s ChatGPT Plugin: Cloud Risk Context in Chat and Codex
Orca Security's plugin connects ChatGPT and Codex to Orca's MCP server, letting security teams and developers query cloud alerts, attack paths, effective IAM permissions, and code-to-cloud origins directly from chat or a coding agent instead of logging into a console. The post walks through six security-team use cases (exposure discovery, CVE impact triage, alert-to-blast-radius investigation, identity permission review, CISO reporting) and three developer workflows in Codex where alerts are traced back to the Terraform/code that created the misconfiguration and fixed in place.
 orca.securityarticleAdded 2 Oct 2026, published 30 Sep 2026🛡️ Security
- Average AI Bro (@AverageAiBro) on X
Claude Code added a `claude --desktop` command that opens the Desktop app on the current directory or a resumed/continued session, plus `claude plugin configure` to view a plugin's options. Bundled .mcpb MCP servers can now have their settings set at `plugin install --config` time so they start immediately without a manual Configure step. The post also notes CLAUDE_CODE_DISABLE_WEB_FETCH to disable WebFetch and an allowedProviders setting to restrict which API providers a managed machine can use.
x.comthreadPublished and added 30 Sep 2026🧠 AI - Stevan Bogosavljević (@stevyhacker) on X
LokalBot 0.9.2 is a free, open-source local-first assistant that records meetings and screen activity, using five small open-weight models chained together entirely on a MacBook (6.8 GB total): Nemotron 3 for speaker diarization, Qwen3-ASR 1.7B for transcription, LFM2.5 1.2B for sentence completion, Harrier 0.6B for semantic search, and Qwen3.5 4B for recap generation. It exposes this captured 'memory' to Claude Code and Codex through an MCP server or CLI, letting coding agents pull context from past meetings and screen content.
x.comthreadPublished and added 30 Sep 2026🧠 AI - rehan-remade/universal-modder
universal-modder is a set of Agent Skills, a CLI (um) and a shared knowledge base (field notes in knowledge/) that let AI coding agents such as Claude Code, Codex, Gemini CLI, Cursor, GitHub Copilot and OpenCode find a PC game's engine, reverse-engineer its code, build a working mod, generate art/3D/sound assets via the fal MCP server (or a local ComfyUI server), test the mod in the running game, and write a field note for the next agent. It ships worked examples — a weapon/boss pack for Terraria via tModLoader, a new civilization for Age of Empires II DE, and a real-time Minecraft-inside-GTA-V passthrough mod — each documented with a field note of exact versions, routes and gotchas, and agents can open pull requests to grow the shared knowledge base.
github.comrepoAdded 6 Oct 2026, published 30 Sep 2026🧠 AI - feder-cr/invisible_playwright_mcp
invisible_playwright_mcp is an MCP server (and companion Python library, invisible_playwright) that wraps Playwright so an LLM agent can operate a real browser like a human: clicking, typing, scrolling and reading page content, useful for tasks like checking flight fares across a date range where no API exists. It ships a standalone chat+live-browser UI driven by any OpenRouter model, installs as a plugin for Claude Code, Codex and Gemini CLI, and exposes stealth/identity controls (seed-based browser fingerprint, proxy-derived timezone/locale/geolocation, persistent profile directories) via its invisible_core component.
github.comrepoAdded 7 Oct 2026, published 29 Sep 2026🧠 AI  Getting the Source Right, Not Just the Fact: Source-Aware Verification for MCP Agents
A research writeup from Multiverse Computing introducing ProvenanceGuard, a post-generation verification layer for MCP-based LLM agents that checks not just whether a claim is factually supported somewhere in retrieved evidence, but whether it is attributed to the correct source tool or document, a failure mode they call cross-source conflation. Using local models (MiniLM for source routing, a DeBERTa NLI verifier, and a local LLM for claim decomposition) plus a RARR-style repair loop, it was evaluated on 281 real MCP traces from a medical agent, catching 138 of 139 unsupported claims flagged by human experts and correctly identifying the exact source about 86% of the time on held-out data, outperforming four source-blind baseline checkers. The method has already been adopted in NVIDIA's NVFlow finance-agent grounding stage.
 huggingface.cowriteupPublished and added 29 Sep 2026🧠 AI
- Getting the Source Right, Not Just the Fact: Source-Aware Verification for MCP Agents
Multiverse Computing's blog introduces ProvenanceGuard, a post-generation verification layer for MCP-based LLM agents that checks not just whether a claim is factually supported somewhere in retrieved evidence, but whether it is attributed to the correct MCP source — catching a failure mode they call cross-source conflation (e.g., a refund-policy fact wrongly attributed to an account record). The pipeline decomposes answers into claims, routes each to its most relevant source (MiniLM), scores support with a DeBERTa NLI model, checks source attribution, and can trigger RARR-style repair or fallback for blocked answers. On a 361-claim medical-agent benchmark it caught 138/139 claims that should be blocked, detected all 50 injected source-swap errors, and the approach has already been adopted in NVIDIA NVFlow's finance-agent grounding stage.
huggingface.coarticleAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security  The Official Ruby SDK for MCP Reaches Tier 1
The official Ruby SDK for the Model Context Protocol (the mcp gem) became the sixth Tier 1 MCP SDK in September 2026, after TypeScript, Python, C#, Go and Rust. Version 1.2.0 supports the 2026-07-28 spec revision, including the stateless lifecycle, multi round-trip requests and cache hints. The SDK passes 67/67 server and 50/50 client conformance runs, and the post gives install and upgrade steps.
 blog.modelcontextprotocol.ioarticleAdded 30 Oct 2026, published 29 Sep 2026🧠 AI
- openrig — multi-agent Claude Code/Codex orchestration
OpenRig is an open-source local daemon/CLI/TUI/MCP server that orchestrates teams of Claude Code and Codex agent sessions (via tmux) defined declaratively in YAML "RigSpecs." Its own docs disclose a significant trust/permission footprint: it writes workspace-trust settings and status-line/activity hooks into ~/.claude.json and .claude/settings.local.json, pre-writes Codex trust hashes and trusted workspace entries into ~/.codex/config.toml, defaults Claude to --permission-mode acceptEdits and Codex to -s workspace-write, and supports an explicit OPENRIG_YOLO=1 mode that enables Claude's --dangerously-skip-permissions or Codex's -s danger-full-access. It also relays session/activity telemetry to a local daemon endpoint.
github.comrepoAdded 28 Sep 2026🛡️ Security  No Time to Pwn: CVE-2026-72018 Linux Kernel LPE | XBOW
XBOW's technical write-up on CVE-2026-72018, an out-of-bounds write in the Linux kernel's SMC-D/DIBS loopback code (dibs_loopback driver) that lets an unprivileged user with CAP_NET_ADMIN escalate to root. The bug stems from an unvalidated peer-controlled dmbe_idx/dmbe_size offset computation (smcd_conn_save_peer_info -> smc_ism_write -> dibs_lo_move_data memcpy) that XBOW turned into a reliable LPE by MITM-forging CLC handshake fields via nftables NFQUEUE and grooming kernel cred structures with a 16-byte zero-write primitive alone. The post also details where the autonomous agent's reasoning stalled (abandoning a promising MITM idea, confusing write-what-where with a pure zero-write, chasing an unnecessary UAF) and required human intervention, motivating a multi-agent redesign of XBOW's research pipeline.
 xbow.comwriteupAdded 30 Sep 2026, published 28 Sep 2026🛡️ Security
- openrig — multi-agent Claude Code/Codex orchestration
OpenRig is an open-source local daemon, CLI, TUI and MCP server (built on tmux + SQLite) that manages teams of Claude Code and Codex agent sessions as a single persistent system rather than a pile of terminal windows. Topologies (pods, seats, edges) are defined declaratively in YAML (RigSpec/AgentSpec), booted with `rig up`, inspected via a topology TUI, and can be snapshotted/restored, discovered from existing tmux sessions, and messaged across agents (`rig send`, `rig broadcast`, `rig chatroom`). It ships starter topologies (first-project, conveyor, product-team, secrets-manager using HashiCorp Vault) and documents in detail what it writes to Claude/Codex config, trust and telemetry state on the host machine.
github.comrepoAdded 28 Sep 2026🧠 AI - Bridging LLM Agents and Data Spaces: An Architectural Mediation Approach using MCP
This paper proposes an architectural mediation approach, implemented as the "Eunomia Agent," that uses the Model Context Protocol to let LLM agents discover and invoke Data Space services as structured, schema-driven tools without modifying existing data space components. A prototype validates end-to-end interaction — catalog discovery, metadata retrieval, and data service invocation — while preserving governance, policy, and access-control constraints native to Data Spaces. It offers practical architectural guidance for organizations wanting to introduce AI-driven automation into governed, sovereign data-sharing ecosystems while maintaining compliance and interoperability.
arxiv.orgpaperAdded 28 Sep 2026🧠 AI  Holo4: powering generalist computer-use agents
H Company's blog post announcing Holo4, a pair of open-weight agentic models (27B dense and 35B-A3B MoE, built on Qwen bases) trained to operate software through GUIs, code execution, MCP, and APIs interchangeably rather than a single interface. It reports benchmark results on OSWorld 2.0 and AutomationBench against frontier models like Claude Opus 5.5 and GPT-5.6 Sol, describes the training pipeline (an internal "Agentic Task Factory" generating ~10,000 verifiable environments/tasks plus SFT+RL), and also releases Holotron4 Nano, the same post-training recipe applied to NVIDIA's Nemotron 3 Nano Omni. Weights (BF16, FP8, NVFP4, GGUF) and full agent trajectories are published on Hugging Face.
huggingface.coarticleAdded 29 Sep 2026, published 28 Sep 2026🧠 AI- Paper2Agent: research papers as interactive AI agents
Paper2Agent is a multi-agent AI system that coordinates parallel specialist agents to transform a research paper and its code repository into a tested MCP server exposing the paper's methods as callable tools ('agentified' papers). It ships as a skill for coding agents like Claude Code and Codex, and the project demonstrates the pipeline on real papers (TISSUE for spatial transcriptomics, Scanpy for single-cell analysis, AlphaGenome for genomic variant interpretation), each producing a hosted MCP server that a chat agent can call to run the paper's actual scientific workflows.
github.comrepoAdded 27 Sep 2026🧠 AI - L402-over-eth-Layer2
L402-EL2 is an author's proposal and open-source implementation that adapts the Lightning-based L402 HTTP 402 payment pattern to Ethereum L2s, replacing invoices/preimages with a prefunded escrow contract and cumulative EIP-712 vouchers signed per call. It layers macaroons with caveats (tool, max_cumulative, expires_at) for HTTP credentials and attenuation to sub-agents, on-chain session keys with spending caps (ERC-1271/ERC-4337 compatible), and batch settlement, so an agent pays a provider per MCP tool call without a transaction per call. The stated design specifically meters MCP's tools/call, resources/read, and prompts/get while leaving initialize/tools/list free for discovery, aimed at agent orchestrators calling paid LLM APIs like the author's own LightPhon service; contracts are unaudited.
ethereum-magicians.orgwriteupAdded 29 Sep 2026, published 27 Sep 2026🧠 AI - MCP Python SDK v2.2.0
Release notes for MCP Python SDK v2.2.0 detailing several security-relevant default changes: HTTP clients (Client, streamable_http_client, sse_client) now only follow redirects within the same origin, closing a cross-origin redirect trust gap; OAuth clients now validate the authorization server's issuer even on the legacy (non-protected-resource-metadata) discovery path, preventing metadata/issuer mismatch attacks; idle Streamable HTTP sessions now expire after 30 minutes with a 10,000-session cap to limit resource exhaustion; and a new AuthSettings.validate_token_resource setting lets servers reject bearer tokens not issued for them (audience/resource confusion). Deprecation warnings push OAuth provider configs toward requiring an explicit issuer ahead of a 3.0 breaking change.
github.comotherAdded 27 Sep 2026🛡️ Security - Delegation Without Trust: An Empirical Gap Analysis of Identity, Authorization, and Runtime Governance in Multi-Agent LLM Systems
This arXiv paper defines a threat model for multi-agent LLM delegation covering four adversaries (confused deputy, token theft/replay, prompt-injection privilege escalation, compromised sub-agents) and derives eight security requirements for governed agent systems. It shows that LangGraph, CrewAI, AutoGen, and the MCP authorization model each fail to meet the full requirement set, then implements and adversarially tests an authorization broker that blocks all four threats, rejects 0 of 200,000 forged tokens, and confines a compromised sub-agent to a mean of 1.5 reachable actions (vs. 8,100 under bearer delegation) at ~2.6 microseconds per decision. The broker's principles are said to be productized in VotalAI's LLM Shield.
arxiv.orgpaperAdded 26 Sep 2026🛡️ Security - Kong Konnect MCP server: stored prompt injection via analytics data leads to credential/data exfiltration (CVE-2026-13341)
GitHub Security Advisory (CVE-2026-13341) for Kong's mcp-konnect MCP server describes a stored prompt injection vulnerability where a remote attacker crafts malicious request metadata (e.g. User-Agent) that gets stored in Konnect analytics and later returned unsanitized to an AI assistant via MCP tools, potentially causing the agent to exfiltrate sensitive data (plugin configs, secrets, internal hostnames) to an attacker-controlled URL if the client can make outbound fetches. A related path manipulation flaw in control plane/group identifiers allowed requesting unintended Konnect API endpoints with the user's token. The v1.0.0 patch neutralizes untrusted analytics fields, validates identifiers as UUIDs, encodes path segments, and disables raw plugin config output by default.
github.comadvisoryAdded 26 Sep 2026🛡️ Security - Agent Threat Rules (ATR) — open detection-rule standard for AI agent threats
Agent Threat Rules (ATR) is an open, versioned YAML rule format (ATR-YYYY-NNNNN scheme) for detecting AI-agent runtime threats — prompt injection, tool-poisoning, malicious SKILL.md content, and MCP exchange abuse — evaluated by a reference TypeScript engine (with a Python wrapper) shipped as an npm/pip package, CLI, GitHub Action, and Docker scanner with SARIF output. The project positions itself as "Sigma for agent threats," maps rules to OWASP Agentic/LLM Top 10, MITRE ATLAS, and NIST AI RMF, and publishes an extensive (and unusually self-critical) benchmark suite against corpora like garak, PromptBench, and PromptInject, including documented harness bugs and withdrawn recall figures.
github.comrepoAdded 26 Sep 2026🛡️ Security - awslabs/mcp release 2026.09.20260922000649
This is a release changelog for awslabs/mcp, AWS Labs' collection of Model Context Protocol servers covering services like HealthOmics, Aurora DSQL, Bedrock Knowledge Base retrieval, ECS, CloudWatch, billing/cost management, and dataprocessing. This release adds vended metrics tools, SQL parser-based policy guards for Aurora DSQL, agentic retrieval support for Bedrock KB, and fixes several security issues including region validation to prevent SSRF credential disclosure in the CloudWatch server and read-only mode bypass in the MySQL server. It reflects an actively maintained, high-velocity multi-server MCP monorepo used for AWS tool integration with LLM agents.
github.comrepoAdded 26 Sep 2026🧠 AI - Progressive Skill Discovery as Access Control for Tool-Using LLM Agents
Introduces skilder, a framework that enforces access control over enterprise tool access for LLM agents by packaging tools, instructions and limits into roles delivered progressively through a single MCP server, so an agent only ever receives tools it has explicitly learned/unlocked. The paper argues prompt-based policy is merely probabilistic advice, not a hard constraint, and evaluates skilder against flat-context tool selection and multi-agent orchestration across 13 tasks and six models, showing zero unauthorized tool calls or parameter violations (e.g., spending-limit breaches) once agents completed discovery.
arxiv.orgpaperAdded 26 Sep 2026🛡️ Security - Progressive Skill Discovery as Access Control for Tool-Using LLM Agents
Introduces "skilder," a framework that bundles LLM agent capabilities into roles (skills, tools, instructions, and limits) delivered progressively through a single MCP server, so an agent starts with a minimal catalog and only gains tool access as it learns the roles a task requires. This structural approach enforces access control deterministically at the server layer rather than relying on prompt-based policy, addressing context bloat and governance gaps in enterprise tool-using agents. Evaluated against flat-context tool selection and multi-agent orchestration across 13 tasks and six models, showing zero unauthorized tool calls or parameter violations when agents completed the discovery protocol.
arxiv.orgpaperAdded 26 Sep 2026🧠 AI - graygnatconsole/mcp-audit-tool
mcp-audit-tool is a dependency-light Python CLI that statically scans Claude Desktop, Cursor, Windsurf, Cline, Zed, and VS Code MCP configuration files for security issues, including hardcoded secrets, unpinned/rug-pull packages, pipe-to-shell installers, tool-poisoning via hidden instructions in tool descriptions, filesystem servers rooted at '/', and unauthenticated plaintext HTTP MCP endpoints. It auto-discovers configs across macOS/Linux/Windows, produces a security score/grade plus SARIF 2.1.0 output for GitHub Code Scanning, and is built around the OWASP MCP Top 10 categories with a CI/CD example that fails builds on severity thresholds. The roadmap adds live server probing over stdio/SSE for runtime rug-pull detection and an ML-based prompt-injection classifier for tool descriptions.
github.comrepoPublished and added 26 Sep 2026🛡️ Security  Agent Threat Rules (ATR) — Sigma/YARA-style open detection format for AI agent threats
Agent Threat Rules (ATR) is an open, versioned YAML rule format for detecting AI-agent security threats — prompt injection, tool poisoning, credential exfiltration, unauthenticated agent execution — positioned as "what Sigma is to SIEM and YARA is to malware." Rules carry permanent ATR-YYYY-NNNNN IDs, declare detection conditions against fields like LLM I/O, tool-call args, or SKILL.md content, and map back to OWASP Agentic/LLM Top 10, MITRE ATLAS, SAFE-MCP, and NIST AI RMF; a reference TypeScript engine and Python wrapper ship MIT-licensed. Governance is transitioning from a single BDFL maintainer to a Technical Steering Committee, and the spec is notably transparent about its own limits, withdrawing previously published per-lane false-positive figures after discovering a tainted benign corpus.
 agentthreatrule.orgotherAdded 26 Sep 2026🛡️ Security
- MCP Python SDK v2.2.0
Release notes for MCP Python SDK v2.2.0, the reference Python implementation of the Model Context Protocol. Key changes: HTTP client redirects are now restricted to the same origin as the endpoint, idle Streamable HTTP sessions expire after 30 minutes (with a 10,000-session cap), OAuth authorization server metadata issuer checks are now enforced on the legacy discovery path, and new deprecation warnings push toward requiring explicit `issuer=` and `validate_token_resource` settings ahead of a 3.0 release.
github.comrepoAdded 26 Sep 2026🧠 AI - Hindsight — Agent Memory That Learns
Hindsight is an open-source agent memory system (MIT-licensed, self-hostable via Docker/Helm or usable as Hindsight Cloud) that goes beyond RAG-style recall by having agents learn through consolidated observations and mental models built from retained facts and experiences. It exposes retain/recall/reflect operations, a built-in MCP server per memory bank, Python/Node/Go/CLI clients, an LLM-wrapper for drop-in memory on OpenAI/Anthropic calls, and reports state-of-the-art results on the LongMemEval long-term memory benchmark, independently reproduced by Virginia Tech's Sanghani Center and The Washington Post.
github.comrepoAdded 26 Sep 2026🧠 AI - CVE-2026-90617 in PentestAgent
VulDB entry for CVE-2026-90617, a remote OS command injection (CWE-78) in GH05TCREW PentestAgent. The flaw is in run_task in interface/main.py of the MCP HTTP Server, affects everything up to commit cf882dab, and has a public exploit. The product uses rolling releases, so no version ranges exist, and the fix is an unmerged pull request. The analysis suggests compensating controls: restrict network access to the MCP server, run with least privilege, and validate input upstream.
 vuldb.comadvisoryAdded 26 Sep 2026🛡️ Security
- CVE-2026-85787 in postgres-mcp-server
CVE-2026-85787 affects awslabs postgres-mcp-server before 1.1.7. The SQL validation component uses an incomplete list of disallowed inputs. Crafted SQL placed in content submitted while an authenticated user interacts with the MCP server can bypass the read-only restriction and modify data in PostgreSQL. The fix is to upgrade to 1.1.7 or later. VulDB's added analysis is generic: it points to SQL injection (CWE-89) and recommends least-privilege database accounts and parameterized queries.
vuldb.comadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-85661 in excel-mcp-server
CVE-2026-85661 affects excel-mcp-server 0.1.8. In stdio mode with EXCEL_FILES_PATH unset, the server does not confine file paths, so a client can pass relative or absolute paths to the read and write tools. That gives arbitrary file read and write with the privileges of the server process. The page classifies it as CWE-22 (ATT&CK T1083) and recommends canonical path checks against a base directory, making EXCEL_FILES_PATH mandatory, and running with least privilege.
vuldb.comadvisoryAdded 26 Sep 2026🛡️ Security  Veeam, Terraform MCP, Django Patch Critical Flaws, Led by CVSS 10.0 Cross-Tenant Bug
The Hacker News roundup covers 11 patched CVEs across three products: Veeam Service Provider Console (CVE-2026-58073, 9.5, unauthenticated managed-agent credential theft; CVE-2026-58072, arbitrary file write to RCE), HashiCorp's Terraform MCP Server (CVE-2026-16498, a 10.0 cross-tenant credential-reuse bug caused by the underlying MCP library not issuing unique session IDs in stateless HTTP mode; CVE-2026-16496 stateful-mode equivalent; CVE-2026-14869 SSRF via header/query-param inconsistency), and Django/GeoDjango (CVE-2026-15307, a spatial-lookup flaw letting GDALRaster write files, reachable by a staff user with view permission on a model with a spatial field, plus a stored XSS, a GEOS DoS, and a language-code DoS). Fixes: Terraform MCP Server 1.1.0+, VSPC 9.3.0.35057, Django 6.0.8/5.2.17; none of the flaws are known to be exploited or listed in CISA KEV as of publication.
 thehackernews.comarticleAdded 26 Sep 2026🛡️ Security
 Marimo Notebook Flaw Could Run MCP Commands Before Cells Execute in Edit Mode
The Hacker News details CVE-2026-75149, a high-severity (CVSS 8.8) code injection flaw in Marimo notebooks where a crafted notebook's configuration could supply an attacker-controlled MCP server command that runs as a local subprocess as soon as the notebook is opened in edit mode, before any cell executes. Marimo fixed it in version 0.23.15 by treating notebook metadata as untrusted and allowlisting configuration, stripping ai/mcp/completion/secrets/server sections; the article also covers the related CVE-2026-67618 (AI base_url exfiltrating API keys via notebook metadata) and the earlier CVE-2026-39987 (unauthenticated /terminal/ws endpoint granting a full PTY shell).
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security Amazon Kiro Prompt Injection Can Exfiltrate Sensitive Data Through Kiro Powers
Mindgard disclosed a prompt-injection vulnerability in Amazon Kiro IDE, fixed in v0.8.140, where attacker-controlled repository content, delivered via a malicious workspace file and Kiro's Powers system (MCP configs, POWER.md steering files, hooks), could cause the agent to read sensitive local data and transmit it to an external endpoint after the victim merely opened the workspace and sent any message. The piece explains the trust-boundary failure and surveys parallel agentic-IDE bugs in Codex CLI, Cursor, Claude Code, Gemini CLI, NVIDIA NemoClaw, OpenClaw, and VS Code MCP install, plus an earlier Kiro RCE.
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security FakeGit Campaign Uses 7,600 GitHub Repositories to Spread SmartLoader Malware
Researchers at Island identified nearly 7,600 malicious GitHub repositories (from ~6,600 fake profiles) making up the "FakeGit" campaign, with over 800 posing as AI Skills or MCP servers (for Gmail, WhatsApp, Databricks, Jenkins, Docker, etc.) to distribute SmartLoader via malicious ZIP files that trigger a LuaJIT loader chain, ultimately deploying the StealC infostealer. The campaign has racked up over 14 million downloads across ~200 repos and 600+ listings on registries like LobeHub, Glama, MCP.so, and MCP Market. The report also introduces "AgentBaiting," a technique where AI agents (Claude Code, Gemini, ChatGPT were shown to be susceptible) autonomously discover and surface these malicious repos while searching for skills/MCP servers on a user's behalf, without ever being given a link.
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security Critical Cursor Flaws Could Let Prompt Injection Escape Sandbox and Run Commands
Cato AI Labs disclosed DuneSlide, two critical (CVSS 9.8) Cursor flaws — CVE-2026-50548 and CVE-2026-50549 — that let a zero-click prompt injection (via MCP servers or web search results read by the agent) escape Cursor's terminal sandbox and achieve arbitrary command execution. Both abuse the file-write allowlist logic: one via the run_terminal_cmd tool's working_directory parameter, the other via a symlink-resolution fallback that trusts an in-project path when the real-path check fails; both let an attacker overwrite Cursor's sandbox helper binary or startup files like ~/.zshrc to disable the sandbox entirely. Fixed in Cursor 3.0 (April 2), affecting all prior 2.x versions; the piece also situates this alongside earlier Cursor agent-exploitation chains (CurXecute/CVE-2025-54135, MCPoison/CVE-2025-54136, CVE-2026-26268).
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security LiteLLM Flaw CVE-2026-42271 Exploited in the Wild, Chains to Unauthenticated RCE
CISA added CVE-2026-42271, a command injection flaw in BerriAI's LiteLLM AI gateway, to its KEV catalog after confirming active exploitation; the bug lets any authenticated proxy user run arbitrary commands via the MCP server test endpoints (/mcp-rest/test/connection and /mcp-rest/test/tools/list), which spawned attacker-supplied stdio subprocess configs. Horizon3.ai separately showed the flaw can be chained with CVE-2026-48710, a Starlette "BadHost" header validation bypass, to skip authentication entirely and achieve unauthenticated RCE (combined CVSS 10.0), exposing model provider credentials and enabling lateral movement into AI infrastructure. Fixed in LiteLLM 1.83.7 (test endpoints now require PROXY_ADMIN role) and Starlette 1.0.1; the article also notes a prior LiteLLM SQLi (CVE-2026-42208) exploited within 36 hours of disclosure.
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security AutoJack Attack Lets One Web Page Hijack AI Agent for Host Code Execution
Microsoft researchers detailed AutoJack, an exploit chain in AutoGen Studio, Microsoft Research's multi-agent framework prototyping UI, where a browsing AI agent that loads an attacker-controlled webpage inherits localhost trust, letting the page's JavaScript reach an unauthenticated MCP WebSocket handler that runs an attacker-chosen command with no allowlist. The Hacker News independently confirmed the vulnerable handler shipped only in two PyPI pre-releases, 0.4.3.dev1 and 0.4.3.dev2, not the stable 0.4.2.2 release, and it remains unpatched on PyPI even though maintainers hardened GitHub main at commit b047730 after Microsoft's MSRC report. The piece frames this as a generalizable pattern for agent frameworks, localhost checks treated as auth, unauthenticated local control planes, and agents that browse untrusted content, also seen in the ChatGPhish case and Microsoft's Semantic Kernel RCE research.
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security Agentjacking Attack Tricks AI Coding Agents Into Running Malicious Code
Researchers at Tenet Security disclosed Agentjacking, an attack abusing Sentry's public write-only DSN credential to inject crafted error events containing markdown-formatted malicious instructions. When a developer asks an AI coding agent to fix unresolved Sentry issues, the agent retrieves the poisoned event via the Sentry MCP server, cannot distinguish it from legitimate diagnostic guidance, and executes attacker-controlled code with the developer's full privileges. Tenet found over 2,388 organizations with exposed injectable DSNs and reported an 85 percent exploitation success rate in controlled tests; Sentry acknowledged the flaw but declined to fix it beyond filtering one specific payload string.
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security- 973 MCP Packages, 71% Single-Maintainer: A Practitioner
Suzu Labs guide to securing AI developer workflows across three surfaces: AI-generated code (Veracode 45% vulnerable, a formal-verification study at 55.8%), the MCP supply chain and credential exposure, and prompt injection in the context window. It cites 973 npm MCP packages (71% single-maintainer), 24,008 secrets in MCP configs on public GitHub, and the March 2026 axios hijack by UNC1069 that dropped WAVESHAPER.V2 and tampered with MCP configs. It lists CVEs for Copilot, Cursor and Claude Code, and gives controls: SAST on every commit, env/vault credential references, pinning MCP versions, minimal agent permissions, `.cursorignore`/Claude deny rules, and monitoring IDE DNS traffic.
 securityboulevard.comarticleAdded 26 Sep 2026🛡️ Security
- Vulnerability Database - OSV
CVE-2026-91931 is a critical remote code execution vulnerability in Flowise versions before 3.1.4, triggered through the platform's Custom MCP feature which invokes npx to run Model Context Protocol servers. A fix is available in 3.1.4; the flaw scores 9.0 (Critical) on CVSS, indicating an attacker can achieve arbitrary code execution likely via unsanitized input to the npx invocation path.
 osv.devadvisoryAdded 26 Sep 2026🛡️ Security
- CVE-2026-75130: Context7 through 2
CVE-2026-75130 describes a prompt injection flaw in Context7 (through v2.1.2), an MCP server that serves library documentation to AI coding agents. The vulnerability lies in the Custom AI Instructions feature, which fails to sanitize content before injecting it into agent context; attackers can poison these instructions so that a routine documentation lookup triggers the agent to exfiltrate credentials from environment files and delete files on the victim's machine. Researchers at Noma Security and VulnCheck published independent technical breakdowns of the attack chain.
 nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security
- CVE-2026-65695: Office-Word-MCP-Server through 1
CVE-2026-65695 is a path traversal vulnerability (CWE-22, CVSS 4.0 7.6 HIGH) in Office-Word-MCP-Server through version 1.1.11, an MCP server that exposes Word document manipulation tools to LLM agents. Attackers who can influence the filename argument can supply absolute paths or ../ sequences to document open/save operations, bypassing the check_file_writeable and ensure_docx_extension helpers (which do no base-directory confinement or realpath validation) to read or overwrite arbitrary .docx files outside the intended working directory.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-65056: mcp-webresearch 0
CVE-2026-65056 describes a server-side request forgery in the mcp-webresearch MCP server (npm package @mzxrai/mcp-webresearch, v0.1.7), scoring CVSS 4.0 8.3 HIGH. The visit_page tool only validates URL protocol and does not filter private, loopback, link-local, or cloud metadata IP ranges, so an attacker who controls the LLM-supplied URL argument (e.g. via prompt injection) can steer the server's Playwright browser to internal endpoints like cloud instance metadata services and exfiltrate sensitive internal content, including credentials, back into the model context.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-57860: ForgeCode (tailcallhq/forgecode), an AI pair-programming CLI, automatically loads and executes the MCP servers defined i
CVE-2026-57860 describes an arbitrary code execution flaw in ForgeCode (tailcallhq/forgecode), an AI pair-programming CLI that automatically loads and executes MCP servers defined in a repository's .mcp.json on startup without user confirmation. A malicious repo can define mcpServers entries with arbitrary command/args (e.g. bash -c) that spawn under the invoking user's privileges the moment forge is run inside the cloned repo, giving attackers a reliable initial-access and persistence primitive against developers evaluating untrusted code. CVSS 4.0 8.4 HIGH, CWE-829 (inclusion of functionality from untrusted control sphere); a fix commit and VulnCheck advisory are linked.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-55544: NextCRM is open-source customer relationship management (CRM) software
CVE-2026-55544 describes an authorization bypass (IDOR/BOLA) in NextCRM CRM version 0.12.1, where MCP campaign tool handlers accept user-generated Bearer API tokens but query and mutate campaigns purely by object ID, ignoring the authenticated user's ownership scope. A low-privileged user with a valid MCP token can enumerate, read, modify, delete, or trigger/pause campaigns belonging to other users. Fixed in NextCRM 0.12.2.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-52869: The MCP Python SDK, called mcp on PyPI, is a Python implementation of the Model Context Protocol (MCP)
CVE-2026-52869 describes a session-hijacking flaw in the MCP Python SDK (PyPI package mcp) prior to version 1.27.2: the SSE and stateful Streamable HTTP transports (mcp.server.sse.SseServerTransport and mcp.server.streamable_http_manager.StreamableHTTPSessionManager) route requests to existing sessions using only the session_id query parameter or Mcp-Session-Id header, without checking that the requesting principal matches the session's original authenticated bearer-token client. This lets a different authenticated client that learns or guesses a valid session ID inject JSON-RPC messages into another user's MCP session. CVSS 3.1 base score 7.1 (High); fixed in mcp 1.27.2.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-49291: mcp-memory-service is a semantic memory layer for AI applications
CVE-2026-49291 affects mcp-memory-service prior to version 10.65.3: its HTTP MCP JSON-RPC endpoint at /mcp only enforced OAuth 'read' scope before dispatching tools/call requests, so a client holding only read access could invoke mutating tools like store_memory and delete_memory even though the equivalent REST endpoints correctly required 'write' scope. The flaw is a classic missing-authorization bug (CWE-862) surfacing specifically in an MCP tool-dispatch layer, scored CVSS 3.1 8.1 (High) with confidentiality unaffected but integrity and availability impacted. Fixed in 10.65.3.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-42271: LiteLLM is a proxy server (AI Gateway) to call LLM APIs in OpenAI (or native) format
CVE-2026-42271 describes an unauthenticated-privilege RCE in LiteLLM (versions 1.74.2 to before 1.83.7): the MCP server preview endpoints POST /mcp-rest/test/connection and POST /mcp-rest/test/tools/list accept a full stdio MCP server config (command, args, env) and spawn it as a subprocess on the proxy host, gated only by a valid API key with no role check. Any authenticated user, including low-privilege internal-user keys, could run arbitrary commands on the LiteLLM proxy host. Patched in v1.83.7; also tracked as GHSA-v4p8-mg3p-g94g and affects Red Hat OpenShift AI.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-19984: A flaw has been found in jkawamoto mcp-florence2 up to 0
CVE-2026-19984 describes a server-side request forgery flaw in jkawamoto mcp-florence2 (up to 0.3.13), an MCP server wrapping Microsoft Florence-2 image model. The vulnerable get_images function in src/mcp_florence2/__init__.py passes an attacker-controlled src argument into an HTTP fetch without validation, letting a remote caller force the server to request arbitrary internal or external URLs. The maintainer recommended fix is deploying an SSRF-safe egress proxy rather than patching the source, and a public exploit is available.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-19978: A flaw has been found in jiantao88 android-mcp-server up to cfb872b2446794193b58edd63f4dbf6af48a6292
CVE-2026-19978 describes an OS command injection (CWE-77/78) in jiantao88's android-mcp-server, where the child_process.exec call in build/index.js fails to sanitize the deviceId, packageName, permission, and extras[].key/value arguments used to control Android devices. The flaw allows local command execution and has a published exploit; it was fixed in commit 14e2bf27c88ba137e35cbb0c2a75f72b595bb98a. CVSS 4.0 base score is 1.9 (local attack vector only), and the project uses rolling releases so no fixed version numbers are assigned.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-18655: Improper restriction of intended endpoints in the RabbitMQ broker connection tools of the Amazon MQ MCP Server (awslabs
CVE-2026-18655 describes an improper endpoint restriction flaw (CWE-923) in the RabbitMQ broker connection tools of awslabs.amazon-mq-mcp-server versions before 2.0.24. A remote unauthenticated attacker can use prompt injection introduced into the MCP client context to redirect the broker hostname to an attacker-controlled endpoint, causing Amazon MQ for RabbitMQ credentials or OAuth access tokens to be sent there; CVSS 4.0 base score 7.1 (High). Fixed in version 2.0.24, referenced via an AWS security bulletin and a GitHub security advisory (GHSA-xwj6-8x5h-hjp6).
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-16584: Improper handling of an initialization failure in AWS API MCP Server from 0
CVE-2026-16584 affects AWS API MCP Server (awslabs.aws-api-mcp-server) versions 0.2.13 through 1.3.46: if the security policy enforcement data fails to initialize at server startup, the tool silently skips policy checks for the rest of the process's life, letting an agent execute AWS API operations the admin configured the policy to deny or gate. Underlying IAM permissions still apply and are unaffected, but the intended allow/deny gating layer is bypassed (CWE-455, improper handling of initialization failure). Fixed in 1.3.47.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-16498: The terraform-mcp-server before version 1
CVE-2026-16498 is a critical (CVSS 3.1: 10.0) exposure-of-sensitive-information flaw (CWE-488) in HashiCorp's terraform-mcp-server prior to version 1.1.0. In stateless streamable-HTTP transport mode, one user's Terraform API token could be reused to execute tool calls on behalf of a different, subsequent user, breaking tenant isolation in shared MCP server deployments. Fixed in terraform-mcp-server 1.1.0; further detail is tracked in HashiCorp's HCSEC-2026-23 advisory.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-14748: A flaw has been found in AIAnytime Awesome-MCP-Server up to a884bb51bcd99e08e14fd712c749d55d9d9a13ab
CVE-2026-14748 is a low-severity (CVSS 4.0: 2.1) server-side request forgery flaw in AIAnytime's Awesome-MCP-Server, specifically in the mcp-wiki/wiki-summary component's server.py, where the url argument is not validated before the server fetches it. A remote, low-privilege attacker can abuse this to make the MCP server issue arbitrary outbound requests; the exploit has already been published via GitHub issues and the maintainer has not responded to the disclosure.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-14541: An authentication bypass and audience confusion vulnerability exists in the Google OAuth provider component of Google mc
CVE-2026-14541 describes an authentication bypass (CWE-287) in the Google OAuth provider of Google's mcp-toolbox for databases v1.4.0, an MCP server that lets LLM agents query databases. When the Google authService is configured with mcpEnabled: true but no explicit audience or clientId, the ValidateMCPAuth pipeline skips audience checks for opaque tokens, so any valid Google OAuth access token — even one issued for an unrelated app — is accepted, letting unauthorized clients reach protected tools and data backends.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - Unauthenticated Administrator takeover exfiltrated via the MCP
GHSA advisory for SiYuan v3.7.1 (CVE-2026-66012) describing how the kernel's POST /mcp route registers 31 MCP tools — including a file tool with full read/write/delete/rename/copy over the workspace — gated only by CheckAuth with no admin or read-only check. When the Publish server runs in anonymous mode (a documented configuration for public docs sites), the Publish reverse proxy attaches an anonymous RoleReader JWT to every proxied request, letting an unauthenticated attacker reach /mcp, exfiltrate accessAuthCode/api.token/cookieKey from conf.json, escalate to Administrator, and plant a malicious Electron plugin (nodeIntegration:true, contextIsolation:false) for RCE on the desktop client. Includes a full working PoC and remediation (CheckAdminRole gate, proxy path allowlist, restricting the file tool).
github.comadvisoryAdded 26 Sep 2026🛡️ Security - "Allowed HTTP Request Domains" Restriction Bypass via AI Agents MCP Connector
n8n's AI Agents module did not enforce the "Allowed HTTP Request Domains" restriction on credentials. A member-level user with use-only access to a shared credential could point an MCP tool at an attacker-controlled URL and run the agent, so the credential secret was sent to an external server. It only affects instances with the agents module enabled via N8N_ENABLED_MODULES and a domain-restricted credential shared with a member. It is fixed in 2.28.1 and 2.27.4, and the advisory rates it High (CVSS v4 7.1).
github.comadvisoryAdded 26 Sep 2026🛡️ Security - Ruby SSE Session Poisoning
A GitHub Security Advisory (GHSA-5p9g-j988-pcwv) documents a session poisoning flaw in the Ruby MCP SDK's Streamable/SSE HTTP transport: the server never validates that a POST to /messages/{session_id} actually belongs to the caller, so an attacker who obtains a victim's session ID (e.g. via logs or network sniffing) can silently execute tool calls whose responses are delivered into the victim's own SSE stream. The advisory includes a working PoC (attacker/legitimate client scripts against the SDK's example streamable_http_server.rb), notes that csharp-sdk and go-sdk correctly bind sessions to user identity while ruby-sdk does not, and distinguishes the bug from the related "Stream Replacement" advisory (GHSA-qvqr-5cv7-wh35), which disconnects rather than poisons the victim's stream.
github.comadvisoryAdded 26 Sep 2026🛡️ Security - Missing authentication on MCP HTTP endpoint allows unauthenticated privileged tool calls
GHSA advisory for jovancoding/network-ai disclosing that its MCP HTTP transport (bin/mcp-server.ts, lib/mcp-transport-sse.ts) accepts JSON-RPC tools/call requests with zero authentication, session, or origin checks, and binds to 0.0.0.0 by default. The PoC shows an unauthenticated attacker can enumerate 22 registered tools and invoke privileged ones - config_get/config_set to read and mutate live orchestrator configuration, agent_list/agent_spawn/agent_stop, token_create/token_revoke, budget_set_ceiling, and blackboard_write/delete - with curl requests against a local Docker deployment. Remediation recommended enforcing bearer-token auth in _handlePost() before dispatch, defaulting to 127.0.0.1 binding, and gating state-mutating tools behind authorization checks.
github.comadvisoryAdded 26 Sep 2026🛡️ Security - DNS TOCTOU race condition causes SSRF protection bypass (`/admin/gateways/test`)
GHSA-9hgc-g3w5-67cm details a DNS TOCTOU race in IBM mcp-context-forge's /admin/gateways/test endpoint: validate_gateway_test_url() resolves and vets a hostname against private/cloud-metadata IP ranges, but the actual request is made with httpx (via ResilientHttpClient), which independently re-resolves DNS at connection time with no IP pinning. An attacker with gateways.read permission can exploit DNS rebinding (short-TTL record flipping from a public IP to 169.254.169.254) to bypass SSRF protections and reach cloud instance metadata, exfiltrating IAM credentials where IMDSv1 is enabled. The advisory notes the codebase already acknowledges the gap in two comments and a tracked TODO (ICACF-15), and recommends pinning the validated IP into the connection.
github.comadvisoryAdded 26 Sep 2026🛡️ Security - Flowise MCP Security Bypass Enables RCE
GHSA advisory detailing three bypasses in Flowise's Custom MCP Server security controls (validateCommandFlags and validateArgsForLocalFileAccess in packages/components/nodes/tools/MCP/core.ts) that combine to achieve remote code execution: an unblocked `docker build` subcommand that pulls and runs a remote Dockerfile, a missing `--yes` long-flag alias on the npx blocklist (only `-y` was blocked) enabling arbitrary npm package execution, and a Unix absolute-path regex that fails to catch double-leading-slash paths (`//root/...`), allowing `node` to execute an uploaded local file. Any authenticated Flowise user (or an API key with chatflow view/update rights) can chain these to fully compromise the host via a prediction API call.
github.comadvisoryAdded 26 Sep 2026🛡️ Security - Insecure cryptographic defaults in oidcProvider: alg=none advertised and plain PKCE accepted by default
GHSA advisory for better-auth (< 1.6.11) documenting that the deprecated oidcProvider() and mcp() plugins publish "none" as a supported ID-token signing algorithm in their OIDC discovery document and default allowPlainCodeChallengeMethod to true, silently rewriting missing code_challenge_method to "plain" — both violating OAuth 2.1/RFC 9700. The fix removes "none" from the metadata, defaults plain PKCE to disabled, and rejects requests missing code_challenge_method instead of downgrading them; @better-auth/oauth-provider was never affected.
github.comadvisoryAdded 26 Sep 2026🛡️ Security  CVE-2026-44895 - GitHub Advisory Database
GitHub advisory for @yoda.digital/gitlab-mcp-server (mcp-gitlab-server): with USE_SSE=true the HTTP/SSE transport has no authentication, sends wildcard CORS headers, and binds to 0.0.0.0. Any network caller or any web page the operator visits can open /sse and POST /messages to drive all 86 GitLab tools (delete_repository, push_files, etc.) using the operator's personal access token. It includes a curl PoC, a CVSS 4.0 vector (~6.3 Medium, effectively High when SSE is enabled) and four fixes: required auth token, loopback bind, a CORS allowlist, and the OAuth roadmap.
github.comadvisoryAdded 26 Sep 2026🛡️ Security- Warning: Vulnerability in Starlette framework and related frameworks like FastAPI exposes millions of servers to authentication bypass, Patch Immediately! | CCB Belgium
Belgian CCB advisory on CVE-2026-48710 ("BadHost", CVSS 6.5), an authentication bypass in Starlette versions before 1.0.1. The Host header was not validated when request.url was rebuilt, so request.url.path could differ from the routed path. Middleware and endpoints that enforce access control on request.url could therefore be bypassed. The flaw affects FastAPI, LiteLLM, vLLM, MCP servers and other Python LLM infrastructure, and may expose stored third-party credentials. The advisory recommends upgrading to 1.0.1 or later and increasing monitoring, and links to the badhost.org scanner and to the GitHub, OSTIF, X41 D-Sec and Ars Technica write-ups.
 ccb.belgium.beadvisoryAdded 26 Sep 2026🛡️ Security
- CVE-2026-87912 and CVE-2026-87913: Missing S3 bucket ownership verification in the AWS Security Agent plugin for aws-agents-for-devsecops and MCP Server
AWS bulletin 2026-105-AWS discloses CVE-2026-87912 and CVE-2026-87913: the AWS Security Agent plugin (aws-agents-for-devsecops, <1.1.0) and its MCP server (<0.2.0) write scan output to a predictably-named S3 bucket (security-agent-scans-<account-id>-<region>) without verifying bucket ownership. An attacker who pre-registers that bucket name in their own account can obtain the victim's private source archive, including embedded credentials and infrastructure state. AWS recommends upgrading to 0.2.0 and manually verifying/pre-creating the scan bucket to prevent squatting.
aws.amazon.comadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-87911 - Read-only enforcement bypass enabling operating system command execution in the SQL validation component of Amazon awslabs postgres-mcp-server
AWS bulletin for CVE-2026-87911, an OS command injection flaw in awslabs.postgres-mcp-server (Python, PyPI) versions before 1.1.7. The server's read-only enforcement in its SQL validation component can be bypassed with a crafted `COPY ... TO PROGRAM` statement, letting an unauthenticated actor run OS commands on a self-managed PostgreSQL host when the configured connection role holds superuser or pg_execute_server_program privileges. Fixed in 1.1.7; AWS also recommends connecting the MCP server with a least-privilege, non-superuser role as defense in depth.
aws.amazon.comadvisoryAdded 26 Sep 2026🛡️ Security - No-Box Vulnerability Analysis: Description-only Detection of Indirect Prompt Injection Vulnerabilities in MCP Servers
This paper proposes no-box vulnerability analysis, a new paradigm for auditing systems using only functionality metadata when neither system access nor runtime interaction is available. The authors build MCPSEC, a prototype that audits Model Context Protocol servers for indirect prompt injection vulnerabilities purely from tool metadata exposed at server registration, evaluating it against 20 widely-deployed MCP servers with 177 tools where human evaluators confirmed 95 vulnerable tools; MCPSEC achieved 98.9% recall versus 84.2% for an LLM baseline, also producing hypothesized exploitation techniques per finding.
arxiv.orgpaperAdded 26 Sep 2026🛡️ Security - ShareLock: A Stealthy Multi-Tool Threshold Poisoning Attack Against MCP
ShareLock is a novel Tool Poisoning Attack against the Model Context Protocol that uses Shamir's secret-sharing scheme to split a malicious instruction into benign-looking fragments distributed across multiple tool descriptions, evading detectors that look for monolithic malicious text in a single tool. A covert trigger planted during a server update reconstructs the hidden instruction, and the authors report over 90% attack success across mainstream LLMs and two MCP clients while evading tool-description-based detection far better than prior single-tool poisoning approaches.
arxiv.orgpaperAdded 26 Sep 2026🛡️ Security - A First Measurement Study on Authentication Security in Real-World Remote MCP Servers
The first large-scale measurement study of authentication security across real-world remote MCP servers, scanning 7,973 live deployments and finding 40.55% expose tools with no authentication at all. For the 119 testable OAuth-enabled servers, the authors built a semi-automated (passive traffic inspection + active dynamic probing) detection framework and derived a taxonomy of nine flaw types across four categories — three MCP-specific (open client environments, dynamic client registration, delegated authorization) and conventional OAuth misconfigurations — finding every tested server had at least one flaw, with dynamic client registration flaws hitting 96.6% of servers and leading to information leakage or account takeover; the work resulted in 9 CVEs via responsible disclosure.
arxiv.orgpaperAdded 26 Sep 2026🛡️ Security - MCPTox: A Benchmark for Tool Poisoning Attack on Real-World MCP Servers
MCPTox is a benchmark for evaluating Tool Poisoning Attacks against LLM agents using the Model Context Protocol, where malicious instructions are hidden in a tool's metadata rather than its output. Built on 45 live real-world MCP servers and 353 authentic tools, it generates 1312 malicious test cases across 10 risk categories via three attack templates, and finds widespread vulnerability across 20 LLM agents: o1-mini has a 72.8% attack success rate, more capable models are often more susceptible due to stronger instruction-following, and even the best model (Claude-3.7-Sonnet) refuses less than 3% of attacks.
arxiv.orgpaperAdded 26 Sep 2026🛡️ Security - respanai/respan-gateway
respan-gateway is an open-source Rust LLM gateway shipped as a single binary with a built-in web UI. It lets OpenAI Chat Completions, Responses, Anthropic Messages and Gemini generateContent clients call any model, translating tools, images and reasoning. It adds named routes, fallback, retries, hedged races, MCP server fronting, per-call pricing, request logs and plugins.
github.comrepoAdded 22 Oct 2026, published 25 Sep 2026🧠 AI - Claude Code Templates Repository
Claude Code Templates (aitmpl.com) is an open-source npx CLI and template catalog offering 100+ ready-to-use agents, slash commands, hooks, settings, skills and MCP server integrations for Anthropic's Claude Code, aggregating contributions from Anthropic's official skills repo, K-Dense-AI's scientific skills, and various community projects (superpowers, wshobson/agents, awesome-claude-code, etc.). Beyond the template catalog it ships real-time analytics for monitoring Claude Code sessions, a mobile chat viewer with Cloudflare Tunnel support, a health-check diagnostic, and a plugin/marketplace manager, making it a practical operational toolkit for customizing and running Claude Code.
github.comrepoAdded 2 Oct 2026, published 25 Sep 2026🧠 AI  ICYMI: August 2026 @AWS Security
AWS Security Blog's August 2026 ICYMI roundup covering 20 blog posts, 23 security bulletins, and 17 code samples. The dominant theme is securing agentic AI workloads on Amazon Bedrock AgentCore, alongside IAM/Cognito updates, S3 over-permission remediation, and a bulletin wave featuring prompt-injection consent bypasses in Strands Agents Tools, an IDOR exposing cross-tenant agent memory, credential-disclosure flaws in MCP servers, and RCE issues such as path-traversal-to-root in amazon-ssm-agent and Zip Slip in awsdac.
aws.amazon.comarticleAdded 7 Oct 2026, published 23 Sep 2026🛡️ Security Static Defenses vs. Dynamic Exploits: Why A2AS Fails at the Runtime
Tenet Threat Labs red-teamed a GPT-4o agent with all five A2AS BASIC pillars enabled and an MCP server. A tool response disguised as HTTP 206 pagination and OAuth steps ("Tool Parameter Injection via Semantic Orchestration Mimicry") led the agent to run a shell script, read credentials.txt and exfiltrate the token. It succeeded in over 80% of runs in November 2025. The authors argue for runtime enforcement based on content trust levels.
 tenetsecurity.aiwriteupAdded 29 Oct 2026, published 23 Sep 2026🛡️ Security
 Top 10 attacks on Claude Code and what each one actually broke
Adversa AI catalogs ten distinct Claude Code attacks documented between September 2025 and September 2026: the Miasma supply-chain worm that hit 73 Microsoft repos via a SessionStart hook, TrustFall's unsandboxed MCP server execution on folder-trust, Check Point's CVE-2025-59536/CVE-2026-21852 pre-trust-dialog code execution and API key theft, Sentry-DSN-based "Agentjacking" prompt injection via fake bug reports, a 50-subcommand cap that silently disables deny rules, the SymJack symlink-to-config-hijack primitive working across six agent CLIs, Wiz's GhostApproval deceptive-approval-prompt finding (with CVE-2026-12958 at AWS and CVE-2026-50549 at Cursor but none at Anthropic), the Plugin4Shell SHA/branch-name collision bypassing plugin pinning, an academic MCP tool-poisoning paper achieving RCE on agent/LLM pairs, and SkillCloak's self-extracting-packer bypass of skill scanners. The piece argues almost none of these are model-behavior bugs - they are trust-boundary and consent failures in the surrounding tooling - and closes by pitching Adversa's own runtime agent security gateway as the fix.
adversa.aiwriteupAdded 7 Oct 2026, published 23 Sep 2026🛡️ Security 30+ MCP CVEs in Two Months: What the Early-2026 Vulnerability Wave Means for Your MCP Supply Chain
Analysis of 30+ CVEs filed against Model Context Protocol servers, clients, SDKs, and proxies in the first two months of 2026, showing the flaws concentrated in plumbing (proxies, registries, transports) rather than tool implementations. It walks through CVE-2025-6514 (CVSS 9.6 RCE in mcp-remote via unsanitized OAuth authorization_endpoint URLs shelled out to launch a browser), the chained Atlassian MCP server CVEs (CVE-2026-27825/CVE-2026-27826), unauthenticated public registries, and a systemic stdio-transport advisory, then ties the findings to the NSA's May 2026 MCP security CSI and the OWASP MCP Top 10.
 bex.coarticleAdded 26 Sep 2026, published 23 Sep 2026🛡️ Security





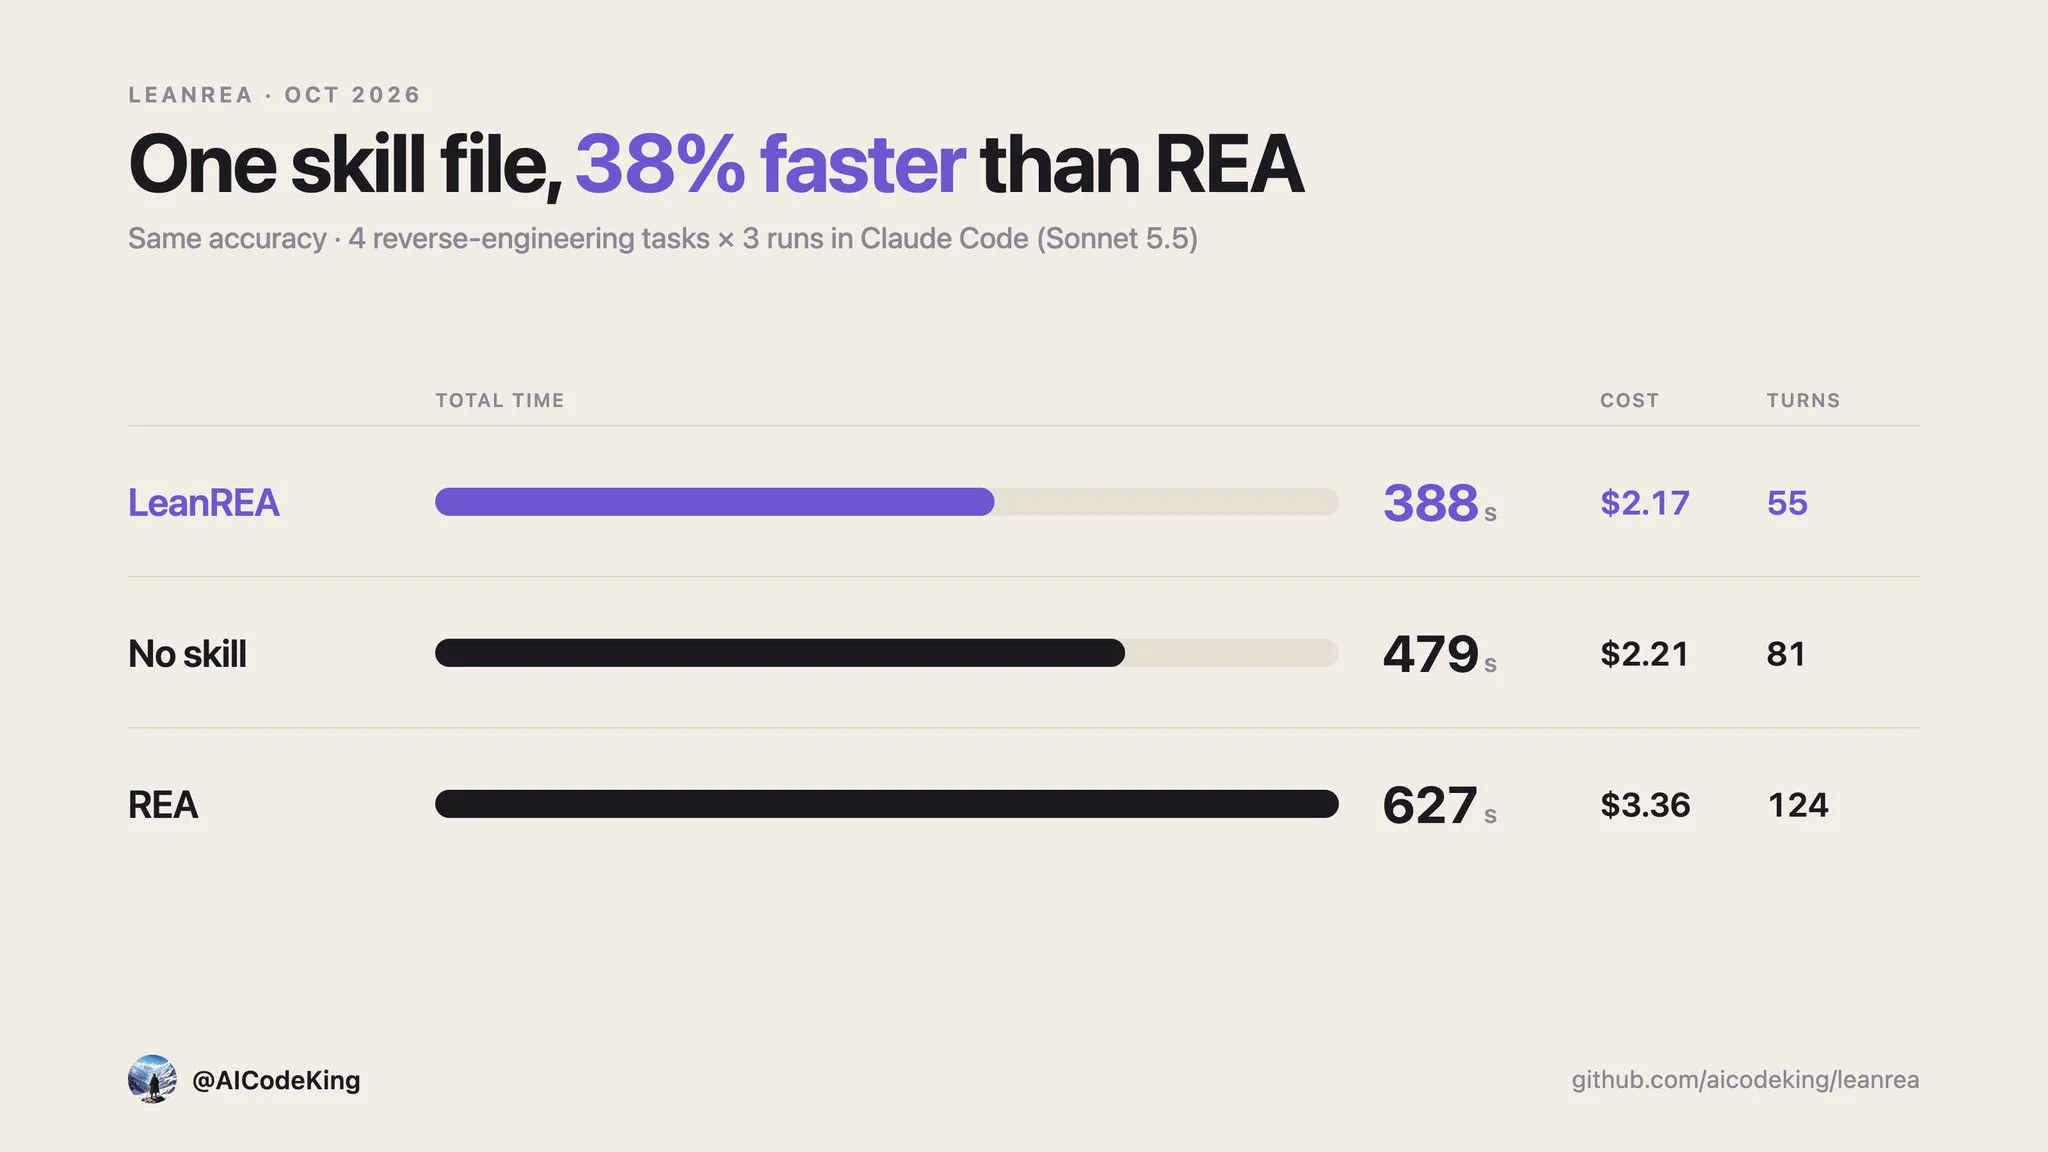


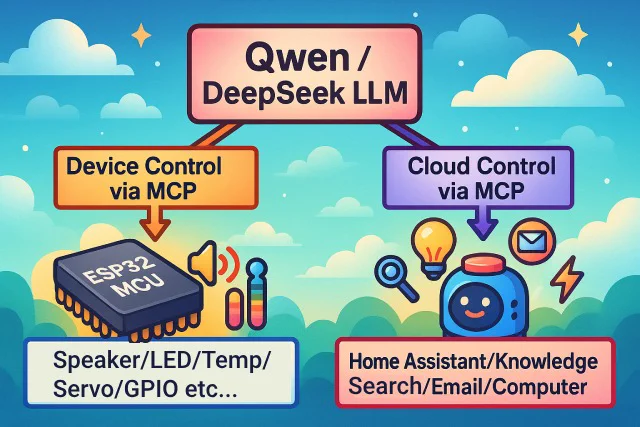



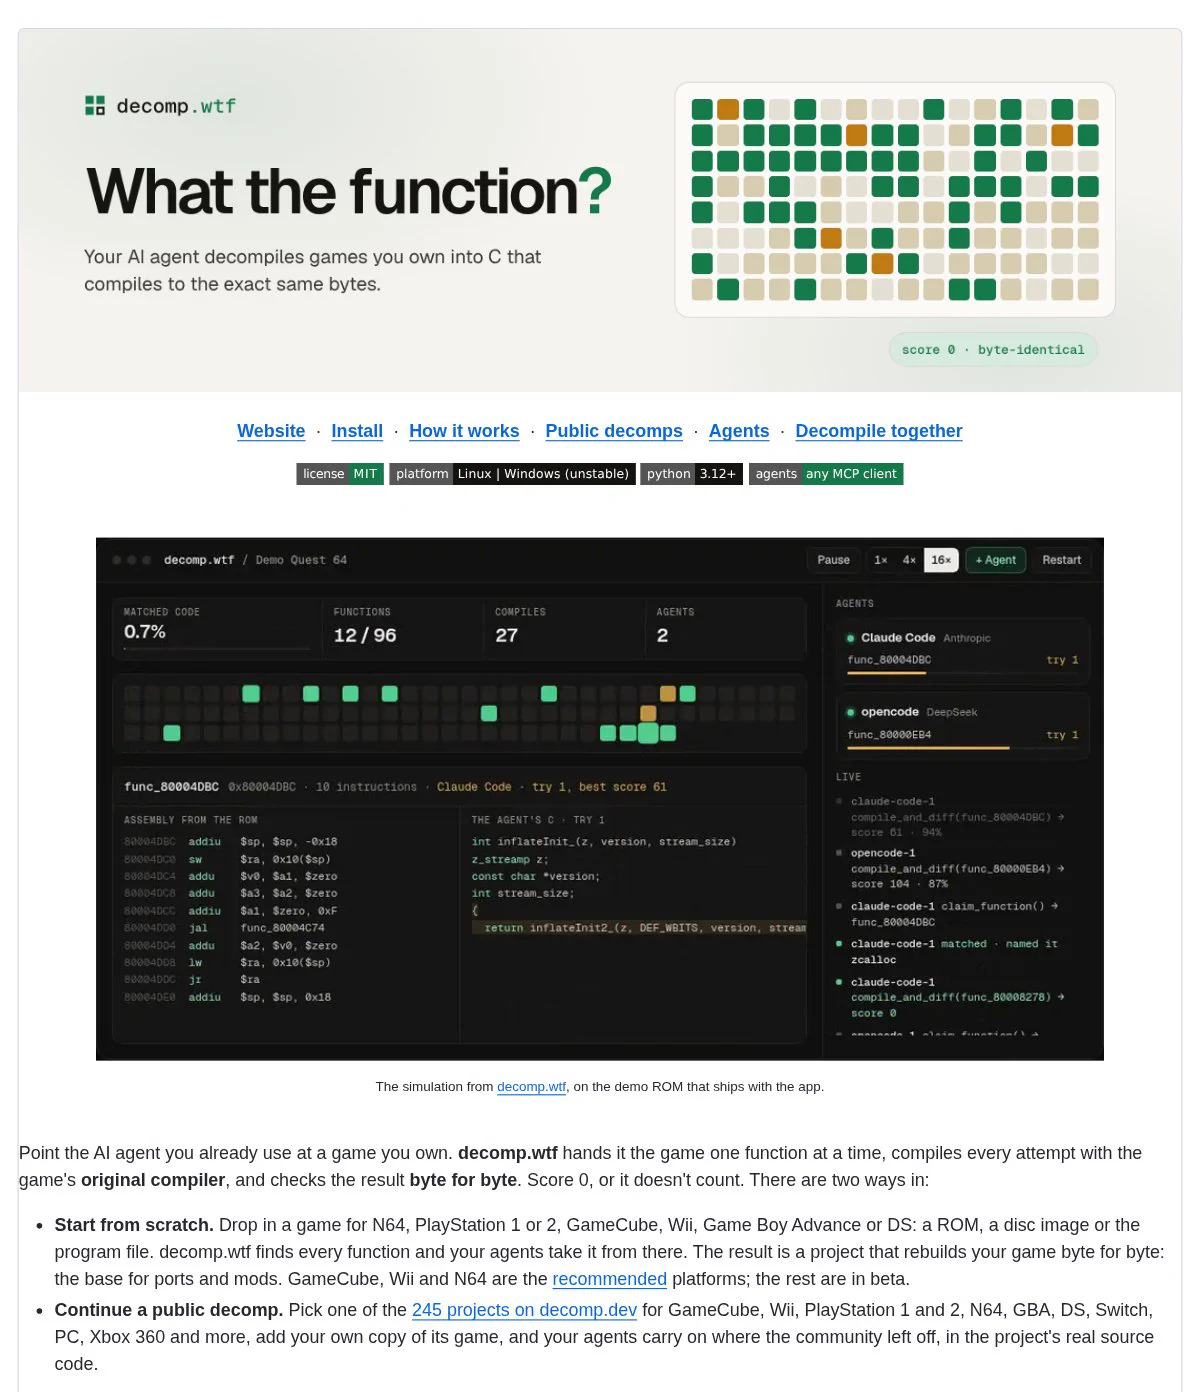


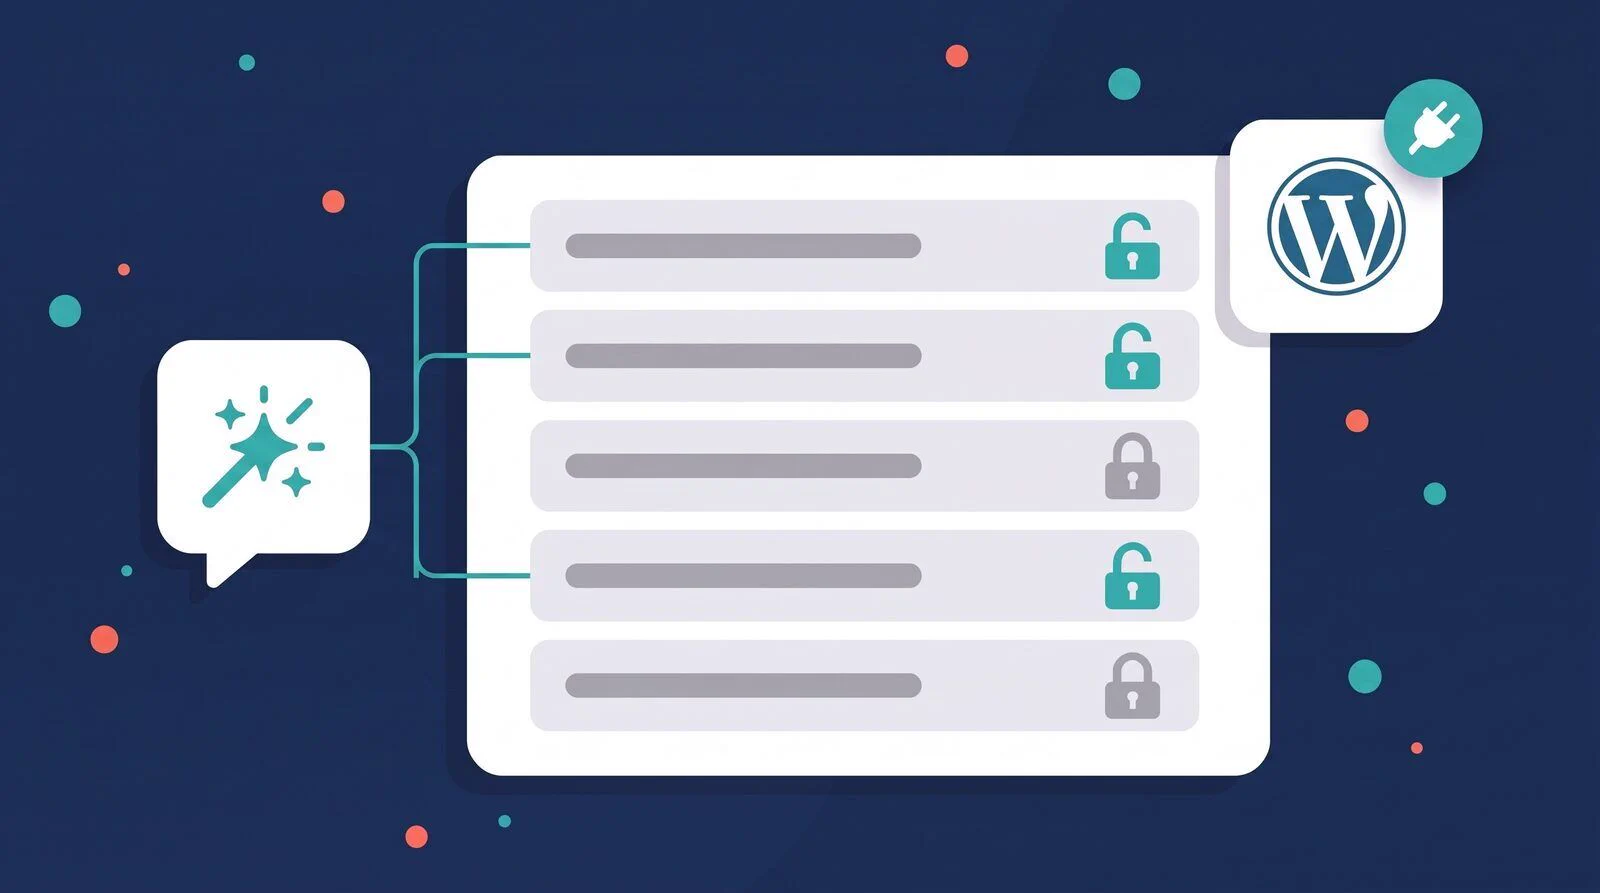


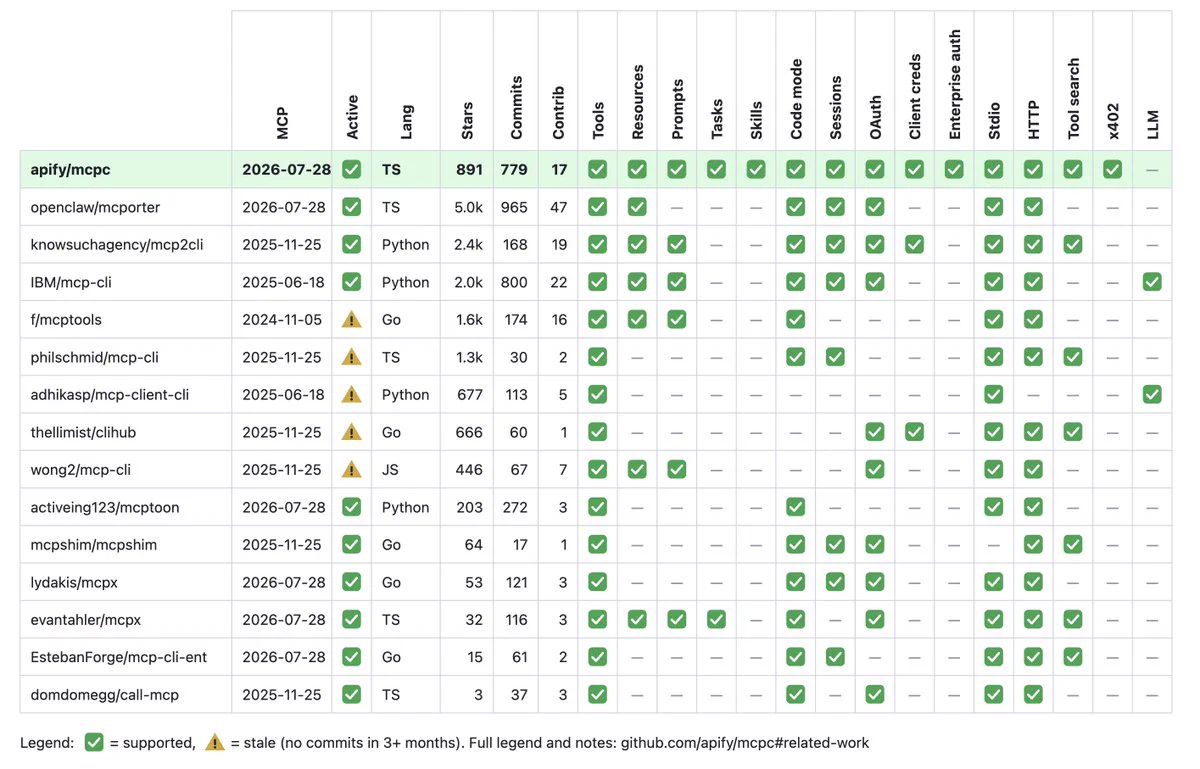


Showing 270 of 515
Show more