 IR trends Q3 2026: Actors impersonate IT help desks in vishing attacks as ransomware activity increases
Cisco Talos Incident Response Q3 2026 trends report. Phishing led initial access at 37 percent, with vishing and IT help desk impersonation to get RMM access; public-facing exploitation followed at 33 percent. Ransomware reached 27 percent of engagements (Qilin, Rhysida, Interlock, new VYPR), with EDR killers via BYOVD and WDAC. It also covers Salt Typhoon intrusions using CVE-2023-20198 and BadCandy, attacks on Claude Code credentials, and logging, MFA and secrets recommendations.
 blog.talosintelligence.comarticlePublished and added 29 Oct 2026🛡️ Security
- Amazon-Themed ClickFix Campaign Serves Up Finger-Licking Malware
Huntress analysis of an Amazon-themed ClickFix campaign that used a Google sponsored result, a fake Amazon login on Google Sites and a fake CAPTCHA to make victims run the Windows finger utility. The .plan script drives IronPython, a Cyrillic-substituted Base64 Python loader, Doina, a Node.js stage, Lumma Stealer via sRDI, and a pirated NetSupport RMM. It lists C2 domains and gives detection tips (aclk/gclid markers, blocking the Run dialog).
 huntress.comwriteupPublished and added 21 Oct 2026🛡️ Security
 US Arrests Two in Crackdown on North Korean IT Worker Laptop Farms
SecurityWeek reports on the arrest of two US nationals (Michael James Bostelle, Juan Cecilio Pena Carrillo) for running laptop farms that helped North Korean IT workers get remote jobs at over 70 US companies, generating more than $3M between 2019 and July 2025. It covers the FBI's Operation Lonestar Roundup (40 Texas locations searched, 187 laptops and KVMs seized). It also covers CrowdStrike's Famous Chollima analysis of shipping-diversion tricks and evolving evasion (hidden RMM tools, spoofed device hashes), and the FBI's 'identity in depth' guidance for spotting ITWs across the employment lifecycle.
 securityweek.comarticlePublished and added 14 Oct 2026🛡️ Security
- Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue RMMs
Huntress details a phishing campaign that abuses legitimate Microsoft Power BI dashboards (app.powerbi.com) to host a fake "Download Reference" lure that bypasses mail filters trusting the Microsoft domain. Clicking the lure triggers browser/environment fingerprinting and Telegram-bot-based victim telemetry exfiltration via attacker domains (dailylifeproject.site, burnsworth.site, etc.), then silently downloads rogue ScreenConnect installers; a chained CMD/PowerShell script (SCAutoFix.ps1) deploys a second ScreenConnect instance, uninstalls the first for evasion, drops the defense-evasion tool HideUL_x64.exe, and sets a recurring scheduled task before Huntress's SOC intervened.
huntress.comwriteupPublished and added 7 Oct 2026🛡️ Security  How Sparse Probability Maps Shape Mixture-of-Experts Routing
This paper trains matched 300M and 1B parameter top-2 mixture-of-experts language models using softmax, 1.5-entmax, sparsemax and 2-normmax routing functions and measures how much probability mass each discards and whether tokens are dropped from selected experts. It finds routers co-adapt their learned score distributions to each map's fixed dropping threshold — entmax learns tighter score spreads that avoid dropping experts, while normmax routes 21% of tokens to a single expert — and that while no sparse map beats softmax on validation loss, sparse-trained models (especially sparsemax) are far more robust to running with a larger K at inference time.
 arxiv.orgpaperAdded 6 Oct 2026, published 5 Oct 2026🧠 AI
- Huntress Tragic Quadrant: Top Cyber Threats Wrecking Businesses
Huntress's "Tragic Quadrant" ranks the cyber threats its SOC sees most often against small/mid-sized businesses by prevalence and blast-radius risk, drawing on 2026 telemetry from 5M+ endpoints and 15M identities. It highlights RMM abuse (45% of endpoint incidents in Q1 2026), mailbox-rule manipulation feeding BEC (24.6% of ITDR signals), AiTM session-token theft bypassing MFA (18.9% of identity threats), plus device code phishing (the EvilTokens PhaaS kit hit 344 orgs in 16 days using Railway-hosted infrastructure and spoofed Cisco/Trend Micro/Mimecast redirect links), ClickFix clipboard-paste infections leading to LummaC2 infostealer compromise, and emerging AI-platform abuse (the FakeAgent campaign hosted a malicious Claude Artifact on claude.ai to drop SectopRAT, hitting 29 organizations in two days).
huntress.comarticlePublished and added 1 Oct 2026🛡️ Security  The Fine Art of Frustrating the Adversary
A Cisco Talos Cybersecurity Awareness Month piece in which eight researchers each give a concrete recommendation for frustrating adversaries at different attack-chain stages: honeypot accounts and tarpits for early deception, behavior-based detection engineering (citing MITRE ATT&CK, Summiting the Pyramid, Macro ATT&CK, LUCID) that targets what an adversary must accomplish rather than specific tools, allowlisting legitimate RMM software (flagging AnyDesk, ScreenConnect, Atera as commonly abused by ransomware like Warlock using Zoho Unattended Agent) over unapproved ones, identity/short-lived-credential controls for AI agent sessions referencing an Anthropic report on Claude misuse incidents, and breaking single-point-of-failure dependencies such as a Telegra.ph-hosted C2 dead-drop resolver used by the Amatera stealer and an EtherHiding-based BNB Smart Chain C2 used by ZigCryptoStealer. Each section gives practical, actionable mitigations defenders can apply today.
blog.talosintelligence.comarticleAdded 7 Oct 2026, published 1 Oct 2026🛡️ Security Phishing Abuses RMM Tools for Persistent Access
Microsoft Defender Experts document a July 2026 phishing campaign that delivers a masqueraded but legitimately signed MSP360 RMM installer (v2.5.0.67) via meeting-invite, Zoom, Adobe, and DHL-themed lures hosted on both attacker infrastructure and legitimate cloud services (S3, Cloudflare R2, Dropbox, GitLab, Supabase). After UAC-elevated installation and service persistence, the RMM.Agent.exe service launches PowerShell to silently install a ConnectWise ScreenConnect client via msiexec, which the actor then uses via RunFile to drop credential-theft and reconnaissance tools disguised as Windows/Defender/Phone Link components. A separate July intrusion used FaronicsDeployAgent.exe the same way to deploy ScreenConnect, showing the technique is not MSP360-specific; Microsoft provides IOCs, hunting queries, and mitigation guidance (Application Control, AppLocker publisher rules, ASR rules) but does not attribute the activity.
 microsoft.comwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security
- Ready, Settra, Go: New Settra Ransomware Variant Deploys MeshAgent RMM
Huntress analysts detail two Settra ransomware incidents (July and September) observed in customer environments, documenting the threat actor's use of the MeshAgent RMM for persistence, BYOVD via the gdrv.sys driver, and anti-forensic techniques including Windows Event Log clearing, reagentc /disable, diskpart-based recovery partition removal, and cipher.exe free-space wiping. The post includes specific IOCs — C2 IPs 45.13.122[.]7 and 193.5.65[.]114, the recurring workstation name WIN-LIVFRVQFMKO, and the RESTORE_FILES.txt ransom note — supplementing prior public reporting from MoxFive and SOCRadar on this newer ransomware variant first seen in June.
huntress.comwriteupAdded 22 Sep 2026, published 17 Sep 2026🛡️ Security - Google Doc Sidebar Sends Mac and Windows Users Down Different Paths to Malware
Huntress SOC analysts Ryan Dowd and Jon Semon tore apart a live social-engineering campaign that began with a fake CoinDesk marketing exec DMing a researcher a Google Doc containing a container-bound Apps Script sidebar. The script ran client-side without OAuth consent, exfiltrated victim IP/geolocation/wallet presence via the Telegram API, then routed macOS users to a piped zsh/DMG AMOS stealer chain and Windows users through ClickOnce and PowerShell loaders using three stolen or fraudulent code-signing certificates (a Norwegian company, Discord, and Lenovo). The Windows chain culminated in NetSupport Manager RMM abuse, a Ledger wallet implant, and a self-generated rogue root certificate authority (spoofing Google Trust Services) installed via MsBuild.exe hollowing to silently intercept HTTPS traffic, which the authors flag as the artifact most likely to survive incident remediation short of full reimaging.
huntress.comwriteupAdded 11 Sep 2026, published 15 Sep 2026🛡️ Security - Best Practices for Good Endpoint Hardening | Huntress
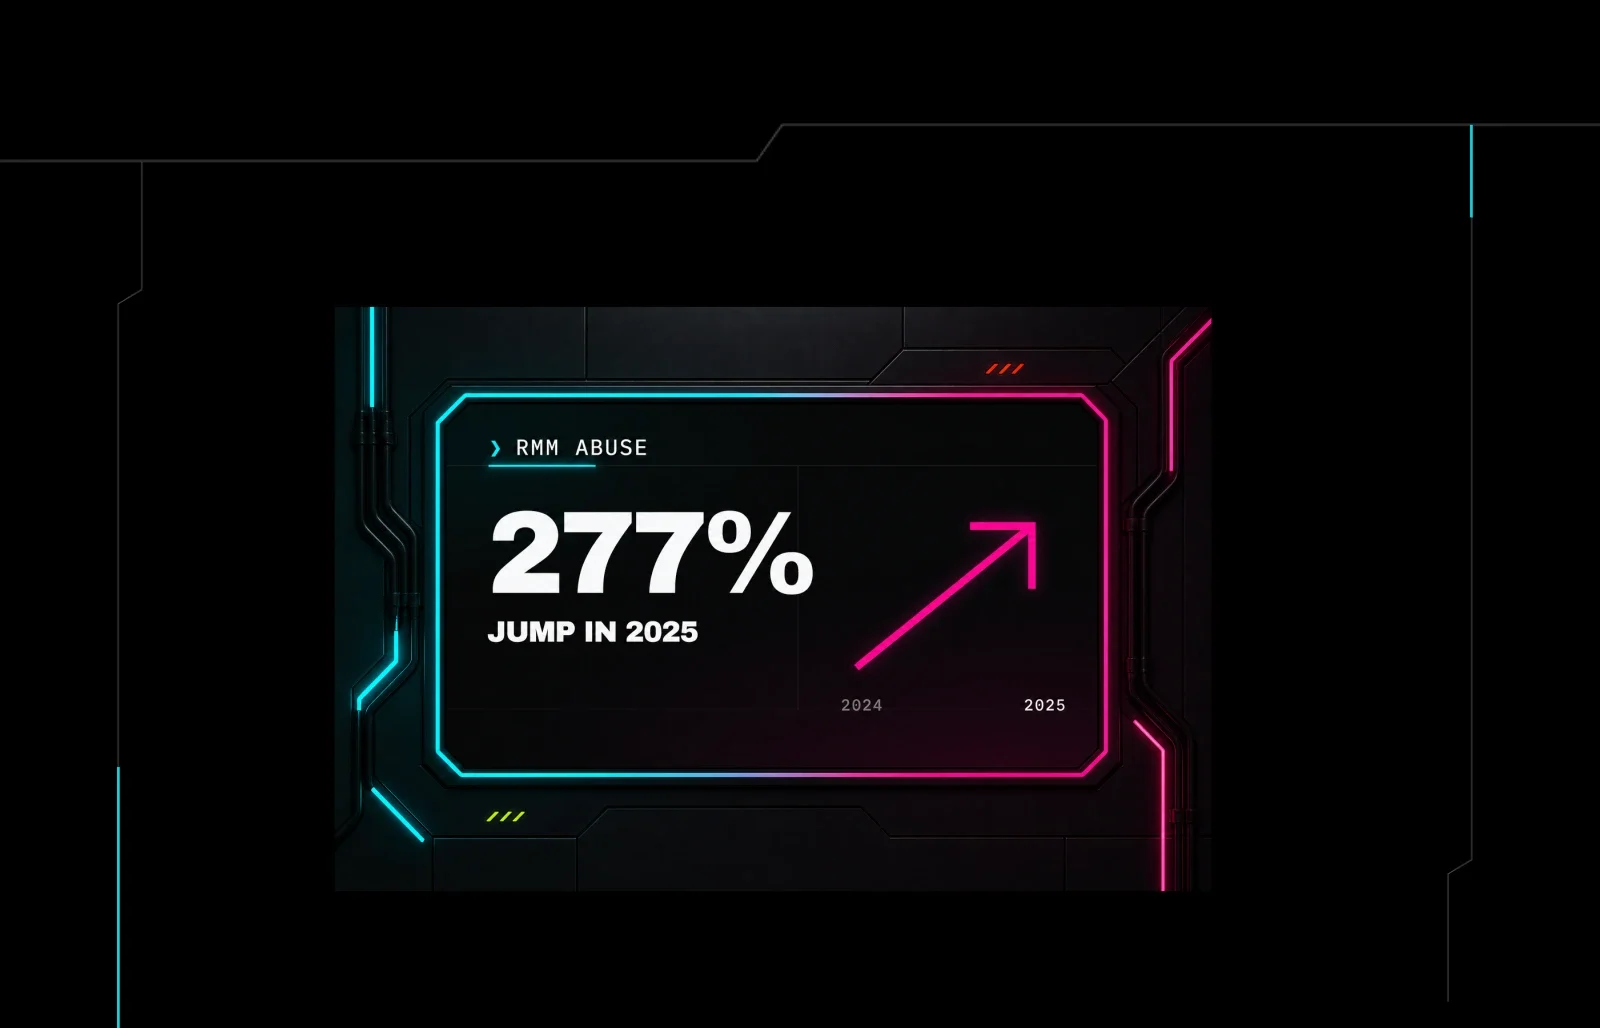
A Huntress SOC-informed guide to endpoint hardening, explaining why checklist-only compliance approaches fail and detailing real intrusion paths observed in incidents: internet-exposed RDP brute-forced by scanners, RMM tool abuse delivered via phishing (277% spike in 2025), and ClickFix attacks that trick users into pasting malicious commands into the Windows Run prompt. It closes with a practical weekly checklist covering external exposure scanning, local admin rights reduction, Windows Defender tamper protection, and disabling SMBv1/legacy protocols.
huntress.comarticleAdded 11 Sep 2026, published 10 Sep 2026🛡️ Security - Phishing Attacks Serve Browser-in-the-Browser Pages, Rogue RMM Persistence
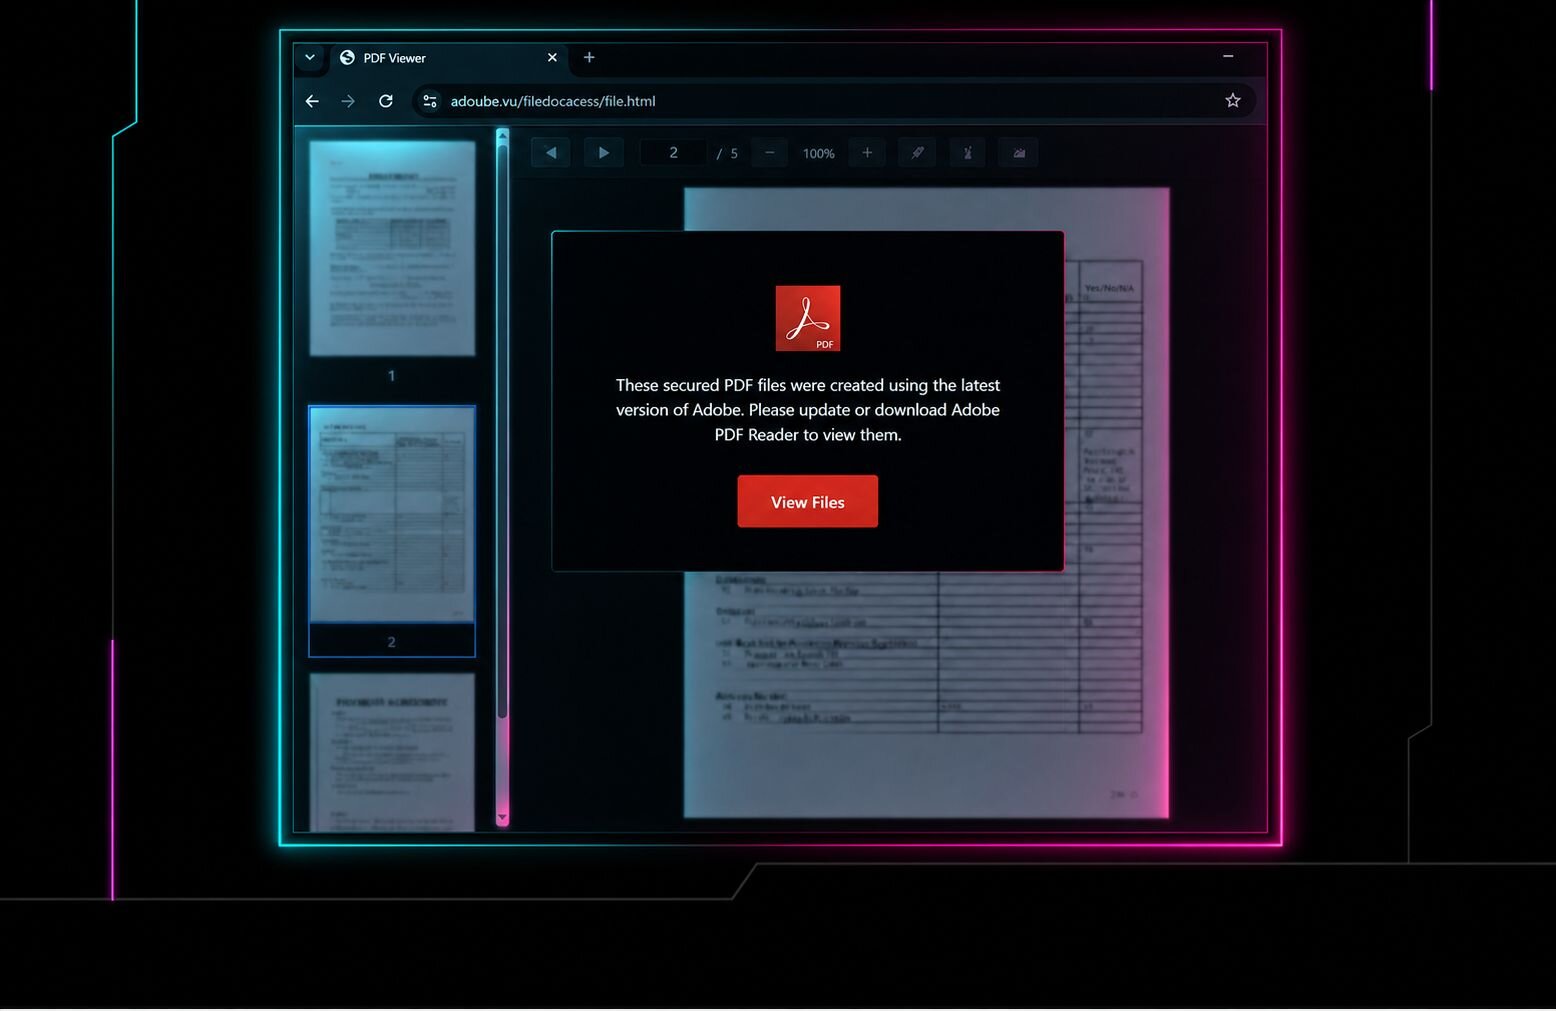
Huntress SOC details two August incidents where phishing emails led victims through a fake CAPTCHA/Adobe PDF Reader lure into a browser-in-the-browser (BiTB) page spoofing get.adobe.com, tricking them into installing a ScreenConnect client disguised as an Adobe Reader update. The installer chained to a second rogue ScreenConnect client via curl/cmd.exe, both registered as Windows services for persistence, then executed defense-evasion binaries (HideCursor.exe, HideUL.exe) to hide cursor/screen activity before Huntress disrupted the intrusions. Full IOCs (domains, ScreenConnect client IDs/relays, file hashes/paths) are included for defenders.
huntress.comwriteupAdded 11 Sep 2026, published 9 Sep 2026🛡️ Security  Financially Motivated Threat Actor BREEZE COMET Targets Brazil
BREEZE COMET (formerly UNC5669) is a financially motivated actor that Mandiant and GTIG track for intrusions into Brazilian banks, fintechs and retailers to make fraudulent Pix, STR and Boleto transfers. The report covers initial access (vishing, RMM tools, compromised government sites, rogue devices), custom backdoors COBALTSPIN, LIGHTPAINT, MILDFROST, KICKPLATE and BOATBEAM, and LLM-assisted scripting. It includes hardening guidance, SecOps rule names and YARA rules.
 cloud.google.comarticleAdded 29 Oct 2026, published 1 Sep 2026🛡️ Security
- RMM Abuse: How Attackers Exploit Remote Access Tools | Huntress
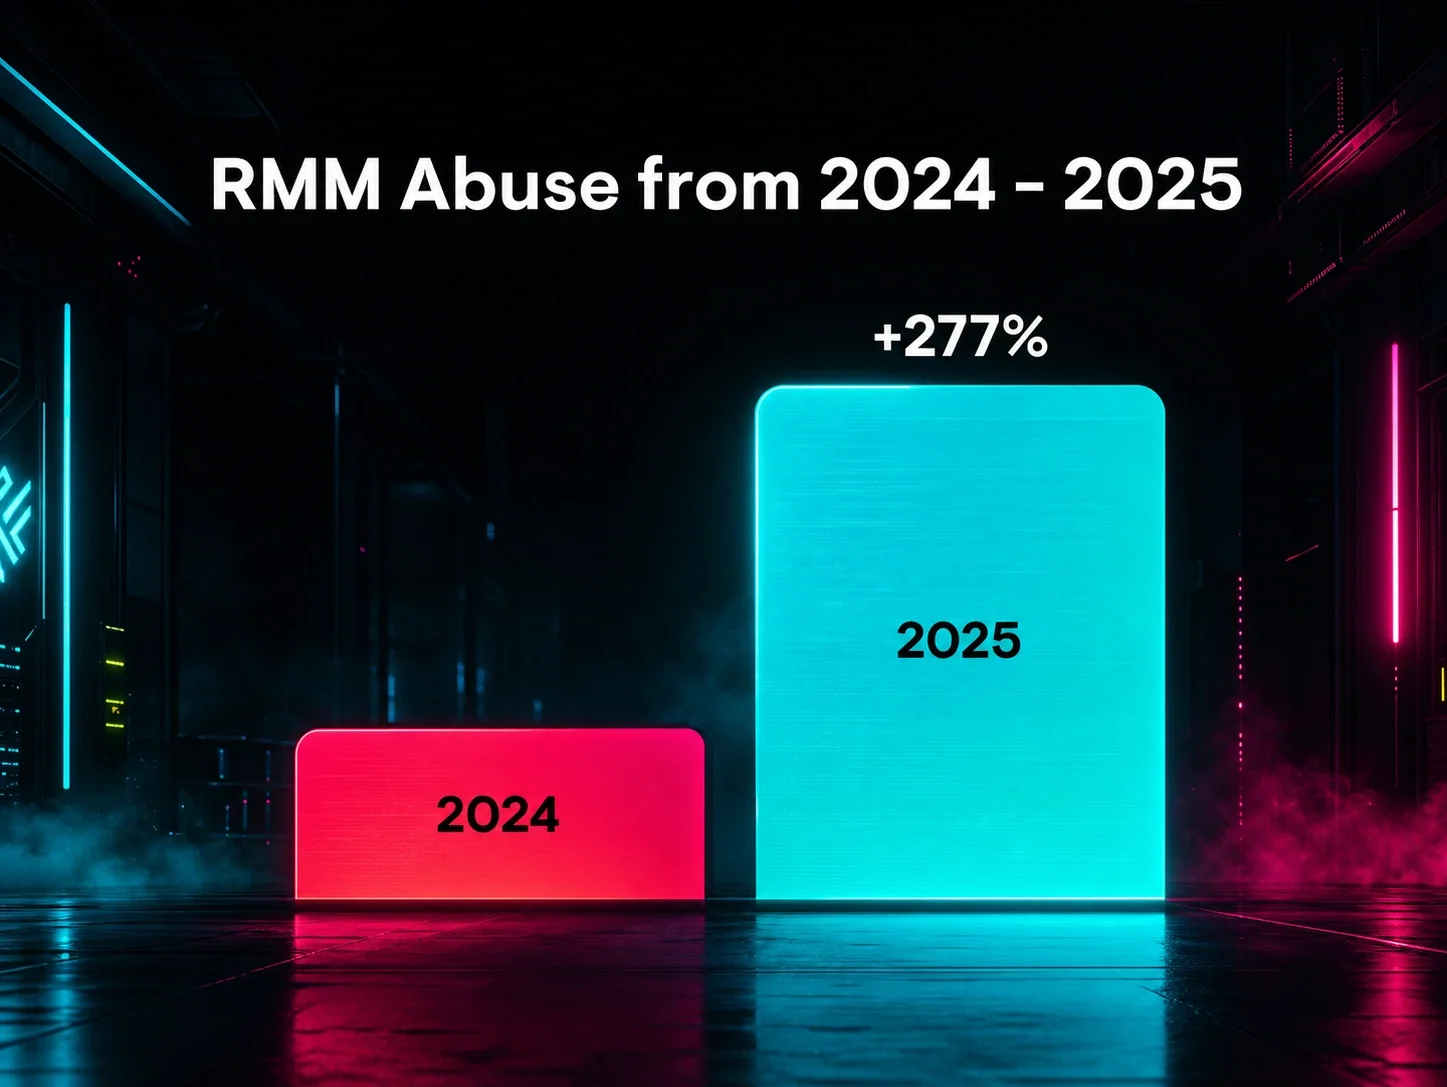
Huntress researchers describe how attackers increasingly abuse legitimate RMM tools like ScreenConnect and AnyDesk instead of custom malware, citing a 277% year-over-year rise in RMM abuse and its presence in nearly 40% of investigated incidents. The piece walks through a real case where a ScreenConnect lure sat dormant for five months before the attacker logged in to hijack a browser session and send spam, and describes how Huntress/AnyDesk staff used RMM access defensively to disrupt an India-based scam call center and a pig-butchering compound. It closes by pitching Huntress's RMM Guard, an app-control feature that inventories and blocks unauthorized RMM installs.
huntress.comarticleAdded 3 Sep 2026, published 21 Aug 2026🛡️ Security - Bank of America Phishing Email Delivers ScreenConnect Malware
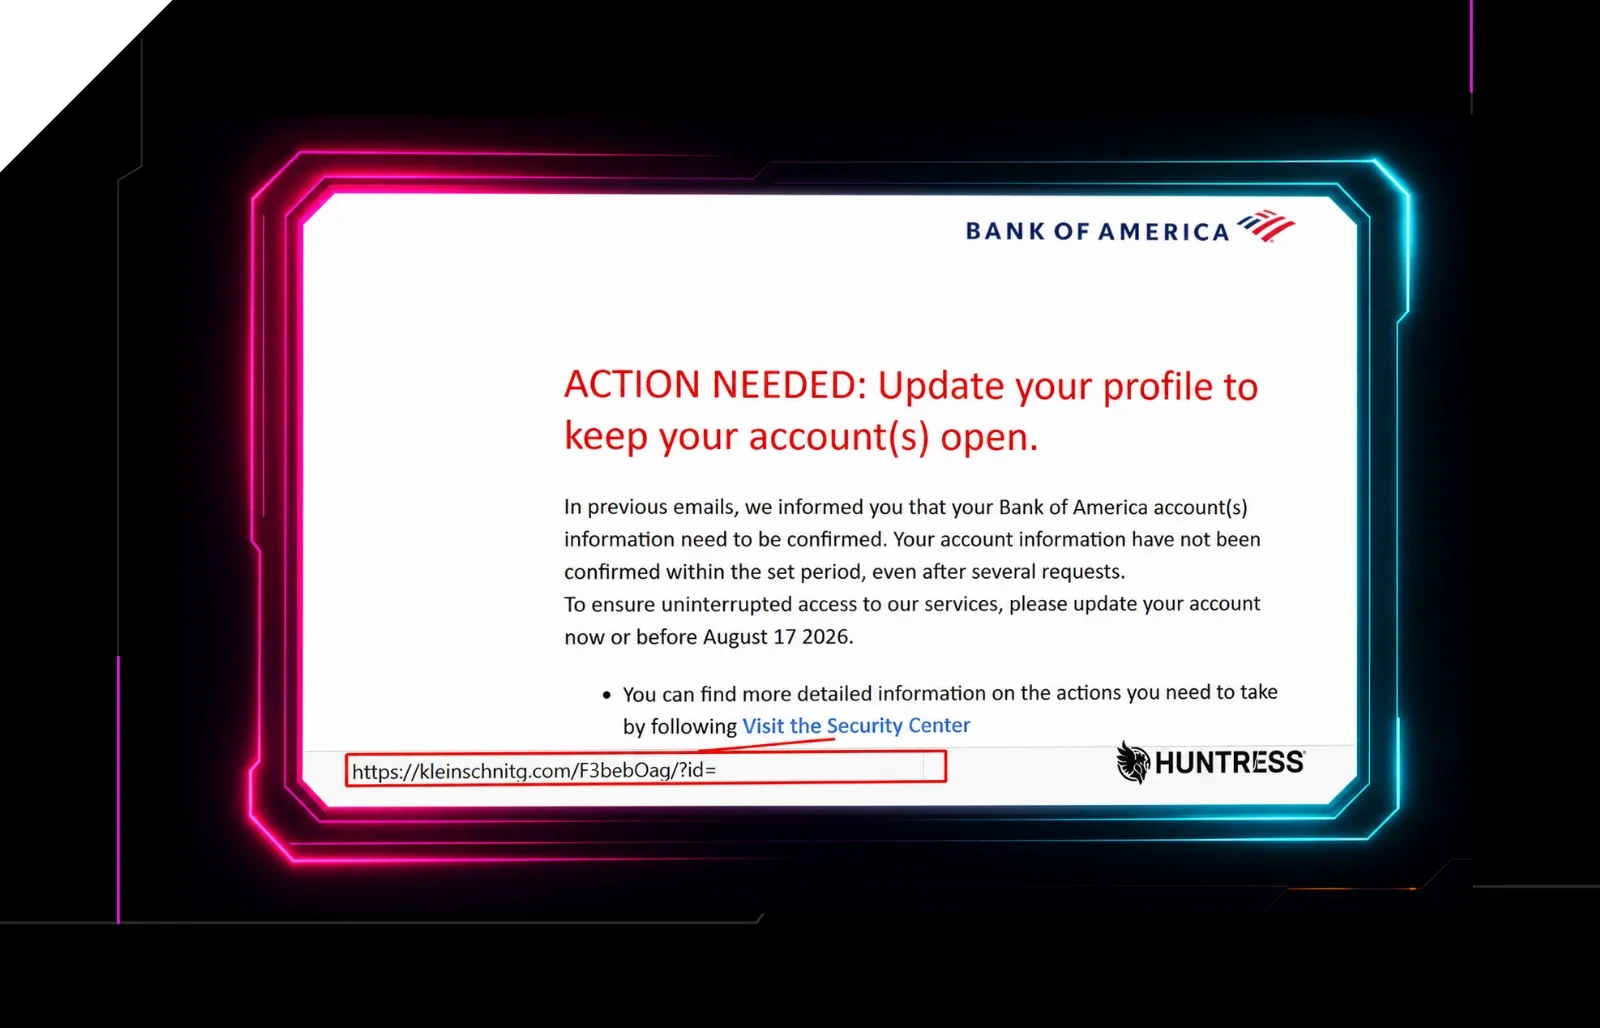
Huntress dissects a Bank of America-themed phishing email that lures victims into downloading AccountGuardSetup.vbs, which unpacks through several layers of base64-encoded PowerShell to silently install ScreenConnect RMM with Administrator privileges. The chain uses AES-128-CBC encrypted blobs to deliver a C# UAC-bypass exploit via the ICMLuaUtil COM interface (MITRE ATT&CK T1548.002), then hides the resulting ScreenConnect service (renamed "Windows Security") from users and admins using SDDL/ACL manipulation so it can't be seen, logged, or removed.
huntress.comwriteupAdded 3 Sep 2026, published 4 Aug 2026🛡️ Security - Critical N-able N-central Vulnerability and Active Exploitation
Huntress' running investigation into critical N-able N-central vulnerabilities exploited in the wild, tracking CVE-2026-18556/CVE-2026-18577 (August auth-bypass/account-takeover via incomplete patch) and later CVE-2026-86206/CVE-2026-86207 and a pre-auth RCE zero-day CVE-2026-86218 (CVSS 10.0). The post details reproduced exploit chains abusing N-central's Take Control feature and API to gain admin access and deploy Cloudflare tunnels for persistence, along with IOCs, attacker tradecraft (anomalous ".invalid" account creation, URL-encoded API abuse, VPN exit-node IPs), and concrete log-based detection guidance for MSPs running the RMM platform.
huntress.comwriteupAdded 3 Sep 2026, published 3 Aug 2026🛡️ Security - Every Ransomware Attack Has a Backstory
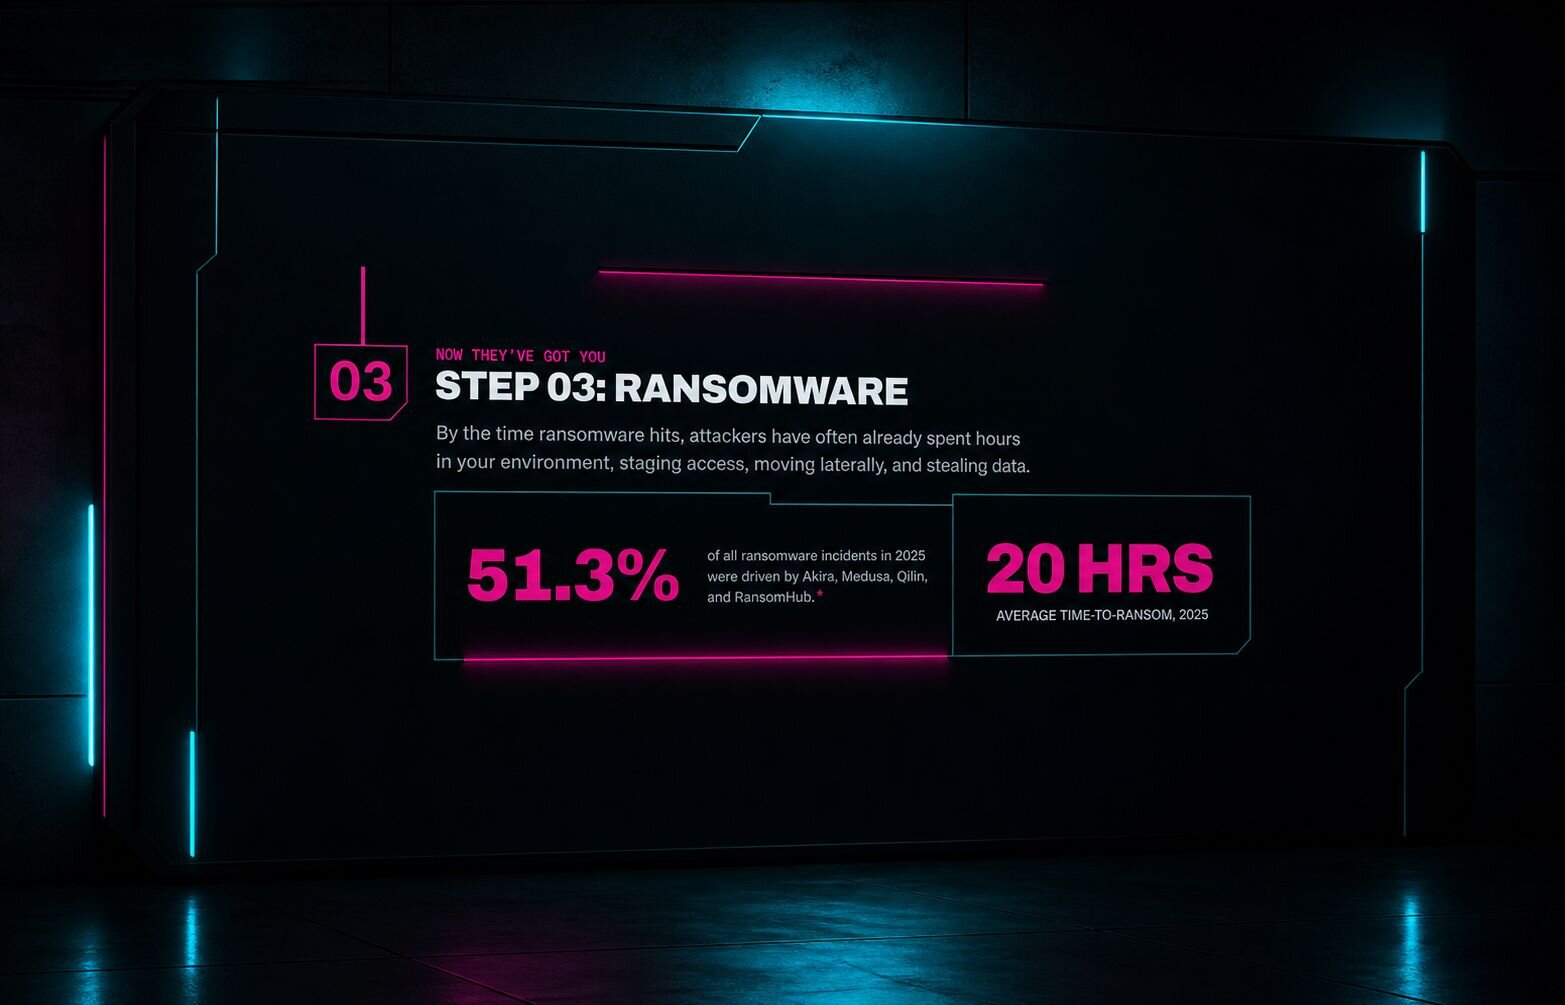
Huntress walks through the ransomware attack chain as a repeatable assembly line: initial access brokers selling footholds (often via infostealers, phishing, or unpatched internet-facing systems), Living-off-the-Land abuse of PowerShell and RMM tools to blend in, and ransomware as the final, visible stage. It cites a real cluster of six ransomware intrusions traced back to the same exposed Citrix NetScaler gateway and session-theft trick culminating in DragonForce ransomware, plus 2026 Cyber Threat Report stats: 37.2% of identity attacks involved suspicious logins, a 277% YoY spike in RMM abuse, ~20 hours average attacker dwell time before detonation, and Akira/Medusa/Qilin/RansomHub driving 51.3% of 2025 ransomware incidents.
huntress.comarticleAdded 3 Sep 2026, published 15 Jul 2026🛡️ Security - 5 Modern Threats You Need to Watch
Huntress details five recurring identity-centered attack patterns seen in its telemetry: credential-based ransomware intrusions that use built-in admin tools for ~20 hours before detonating encryption; Business Email Compromise via inbox rules hiding replies in Conversation History folders; a Qilin ransomware case where attackers impersonated legitimate RMM software, stole browser credentials, and disabled AV; a ClickFix-style social-engineering campaign ("BackgroundFix") that tricks users into pasting a clipboard-hijacked command via a fake "verify you're human" checkbox on a background-remover site; and a shift toward correlation-based SIEM detection that ties together weak brute-force/login signals across VPN, AD, and RDP logs to surface likely intrusions. Each section includes concrete IOC/behavior watchlists for defenders, framing identity (accounts, mailbox rules, device trust, RMM tooling) as the common attack surface.
huntress.comarticleAdded 3 Sep 2026, published 14 Jul 2026🛡️ Security - LoTL Abuse: How to Spot It vs. Normal Admin Activity | Huntress
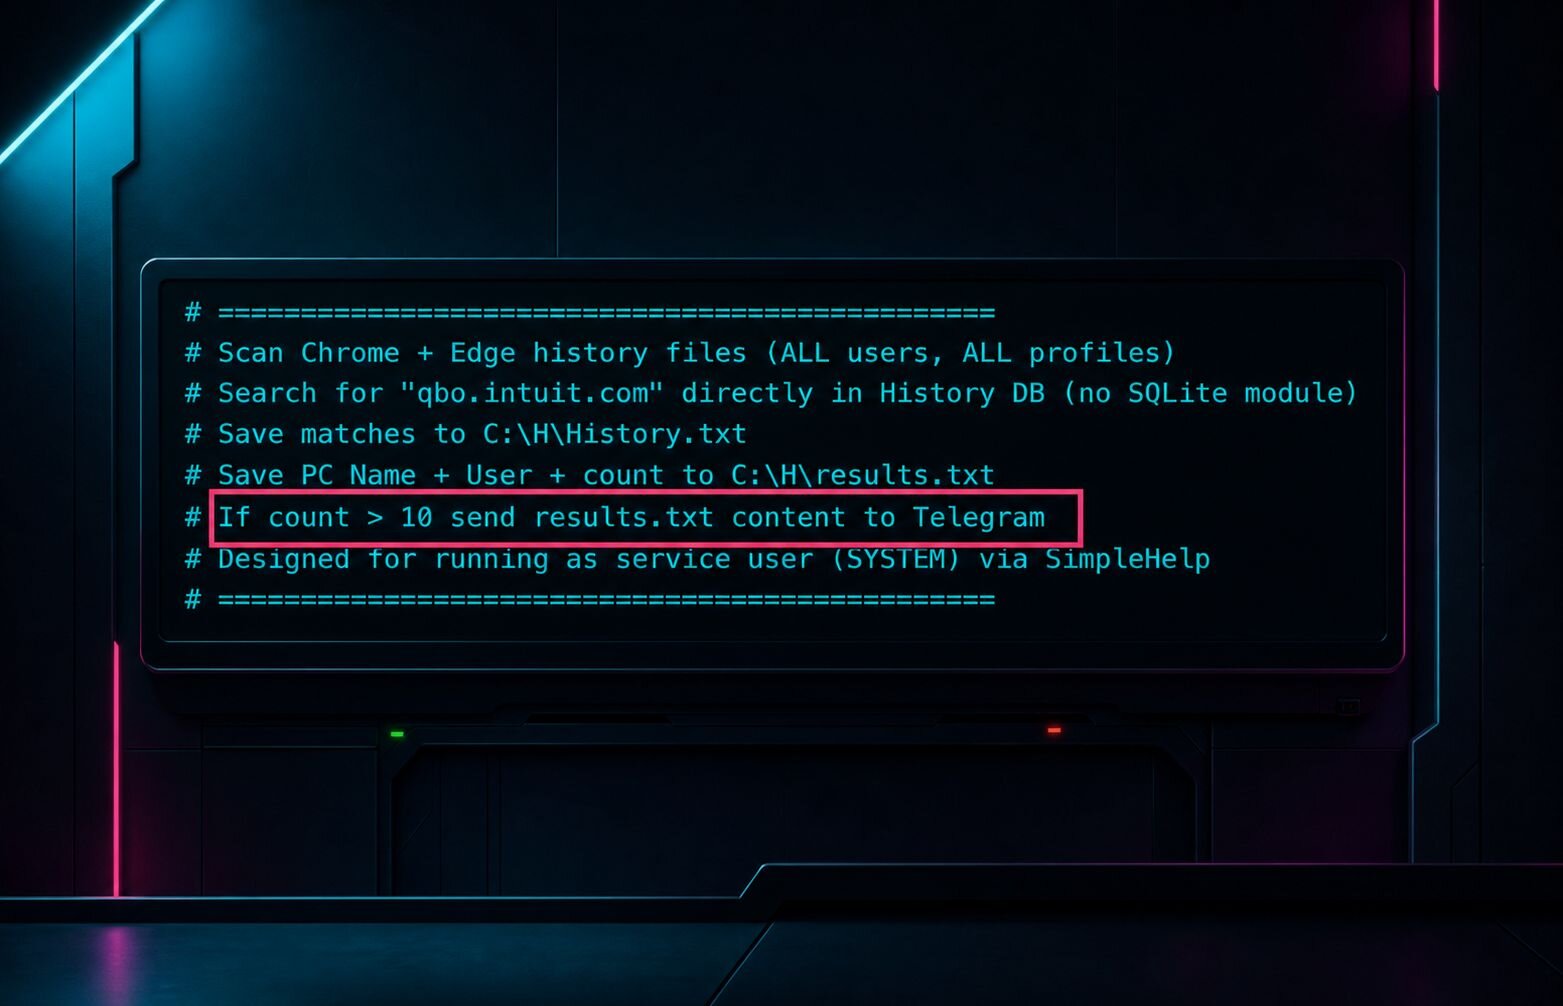
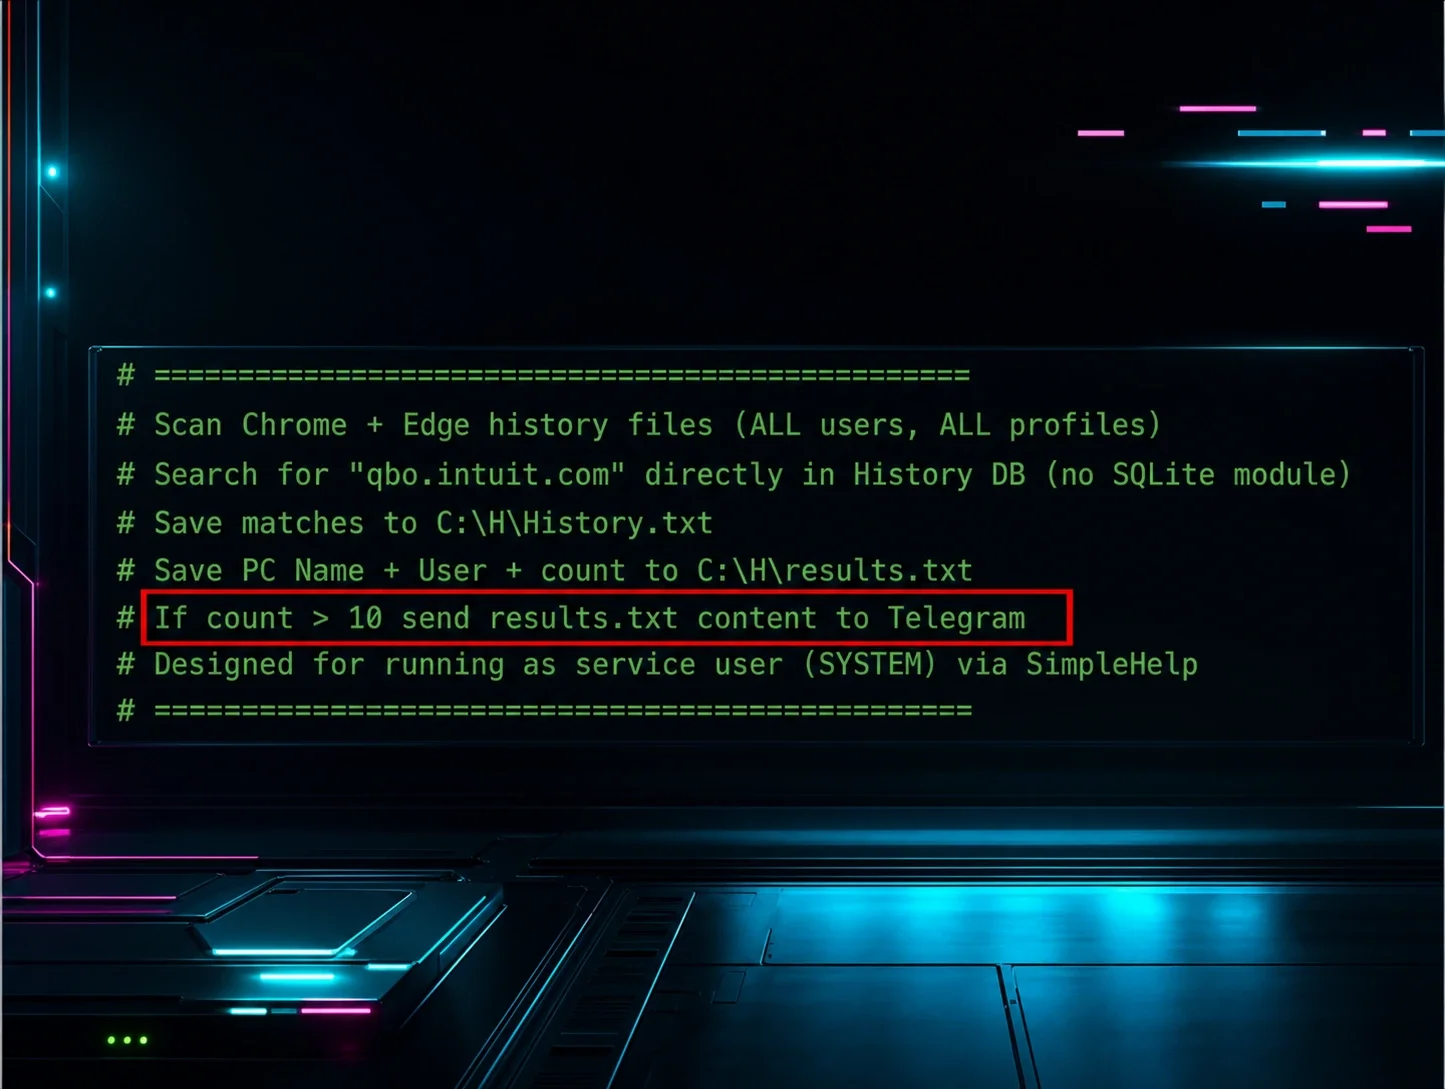
Huntress SOC breaks down how to differentiate legitimate admin use of native tools (PowerShell, WMI, RMM software) from living-off-the-land (LoTL) abuse by attackers, offering a four-point pressure test: who used the tool, where it ran, how it launched, and what followed. It includes real detection examples such as attackers using the legitimate RMM tool Action1 to deploy ScreenConnect for persistent access, a malicious process chain spawning from bomgar-scc.exe, and an LLM-generated script with code comments revealing Telegram-based exfiltration.
huntress.comarticleAdded 3 Sep 2026, published 8 Jul 2026🛡️ Security - Potemkin Loader & RMMProject The Anatomy of a ClickFix Attack
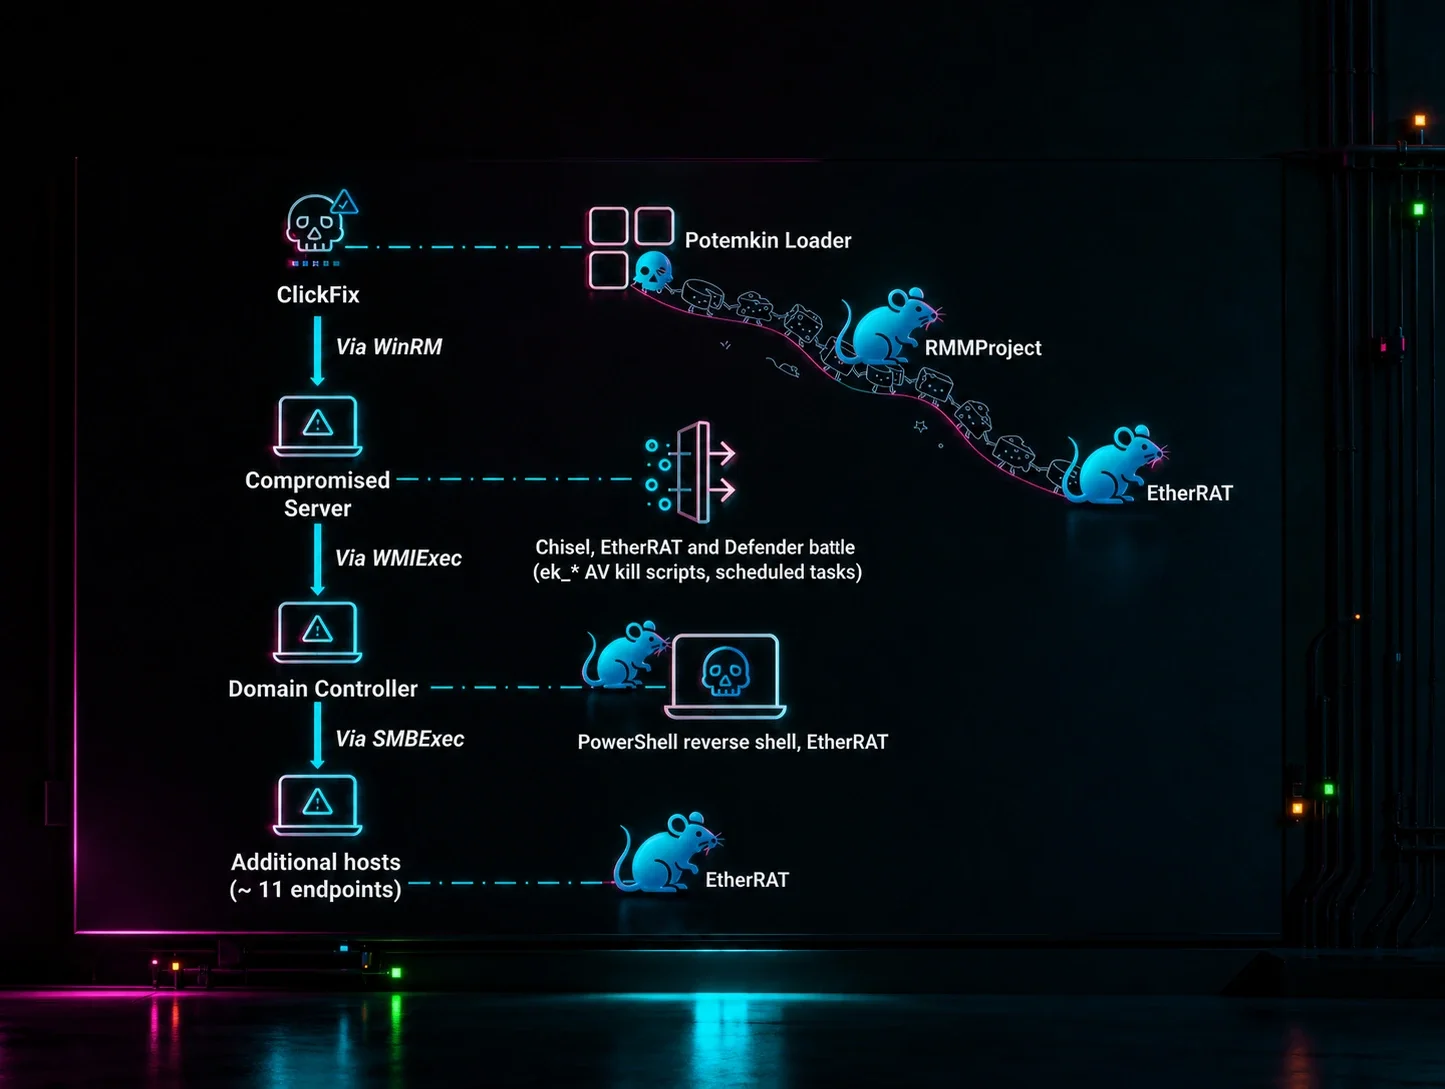
Huntress tears down a May 2026 ClickFix intrusion that escalated from a single unmonitored endpoint to hands-on-keyboard compromise of 11 hosts. The chain starts with a pcalua.exe/mshta.exe LOLBIN abuse to run a remote HTA that silently installs an MSI, dropping Potemkin, a custom x64 DGA-based loader (XorShift32 seed 151678, custom byte cipher, reflective in-memory DLL loading), which fetches RMMProject, a 4.4MB LuaJIT-scriptable module with 15 task types including Chrome App-Bound Encryption bypass via DLL injection into Chrome's IElevator COM interface, Firefox NSS credential theft, and a hidden-desktop remote-control (RTSC) module. The attackers also deployed EtherRAT (an EtherHiding Node.js backdoor resolving C2 from an Ethereum smart contract) and a renamed Cloudflare tunnel client, then moved laterally via WMIExec/SMBExec/WinRM with an AMSI-bypass PowerShell loader to reach the domain controller.
huntress.comwriteupAdded 3 Sep 2026, published 16 Jun 2026🛡️ Security - mthcht/awesome-lists
mthcht/awesome-lists is a large, continually updated GitHub collection of threat-hunting IOC lists: suspicious named pipes, Windows services/tasks/firewall rules/ports, user-agents, mutex names, hostnames, MAC addresses, USB IDs, phishing/sinkholed/dyndns domains, HijackLibs, TOR node lists, LOLDrivers hashes, malicious bootloaders and SSL certificates, VPN provider IP ranges, YARA rules, offensive/greyware tool keyword detection patterns, Microsoft Defender/ClamAV signature lists, and RMM detection artifacts. It also links out to DFIR/threat-hunting courses, labs, and CTF-style datasets (SANS FOR500/FOR508, TheDFIRReport labs, Splunk BOTS, Xintra APT emulation) useful for blue teams building detections or hunting.
 github.comrepoAdded 3 Sep 2026, published 10 Jun 2026🛡️ Security
- Inside the RaaS Ecosystem: Operators, Affiliates & Attack Tradecraft | Huntress
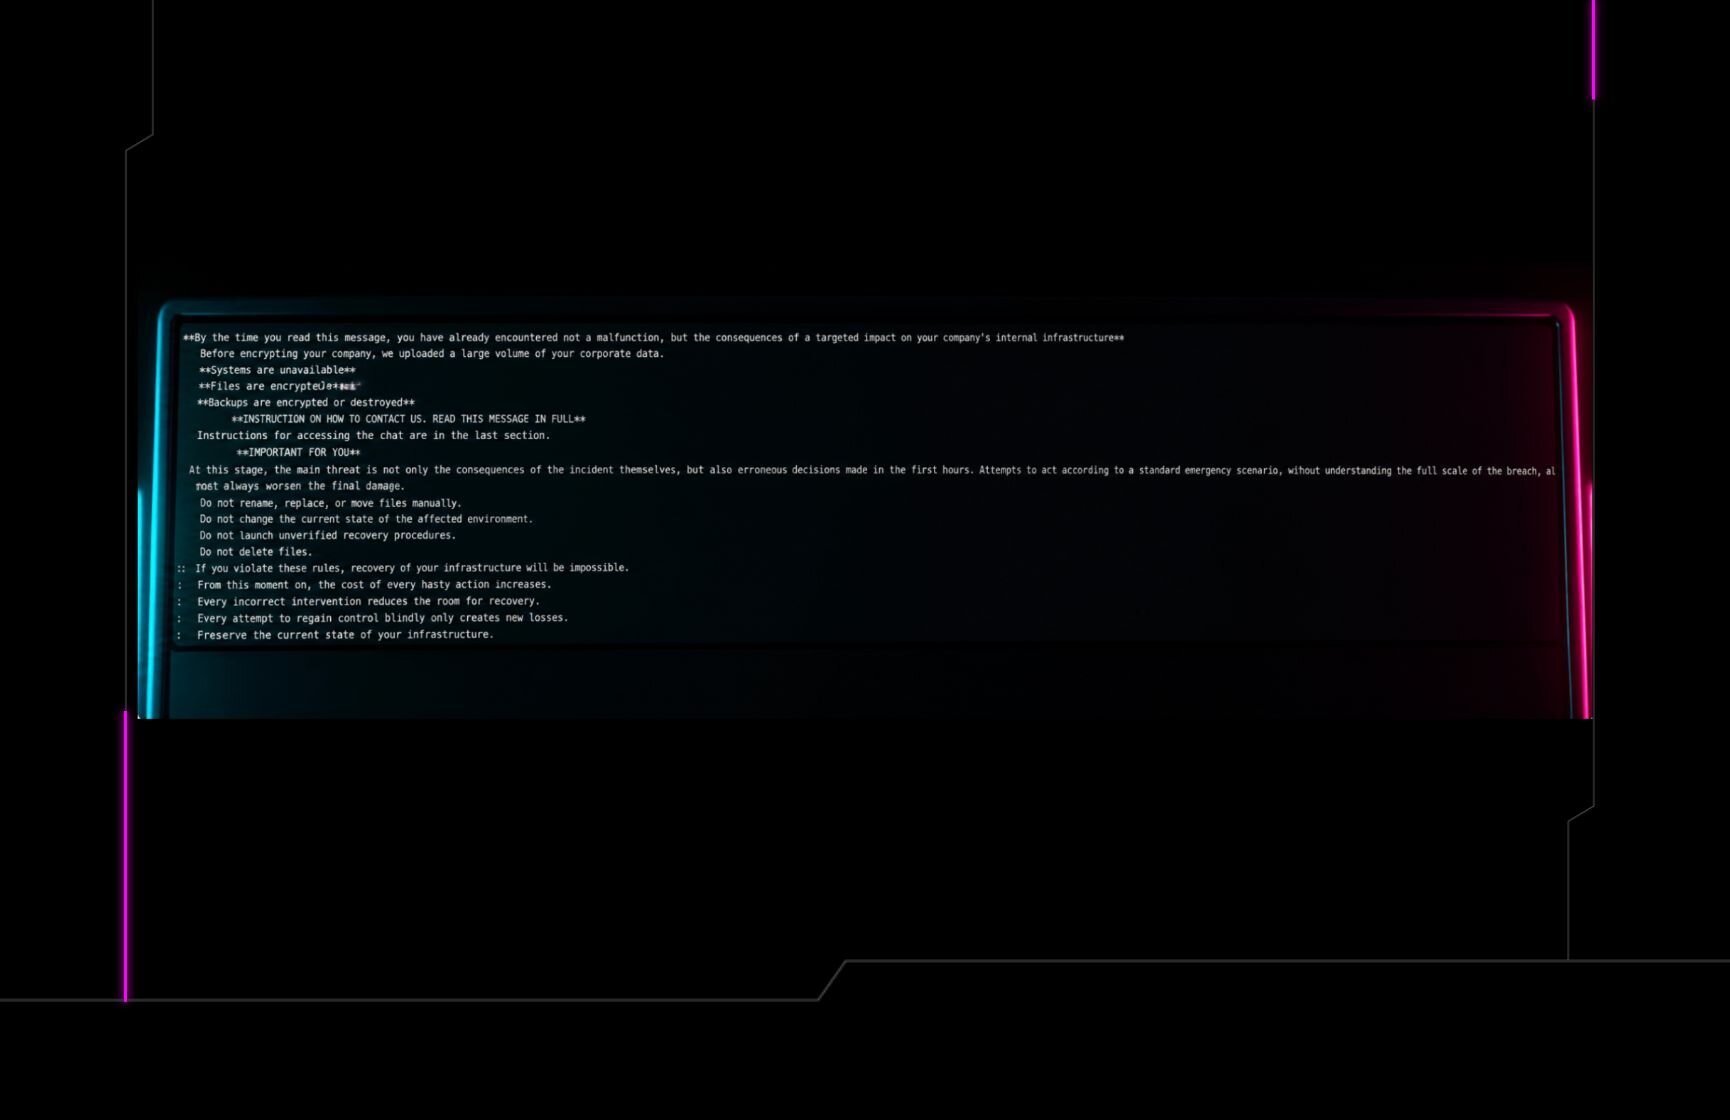
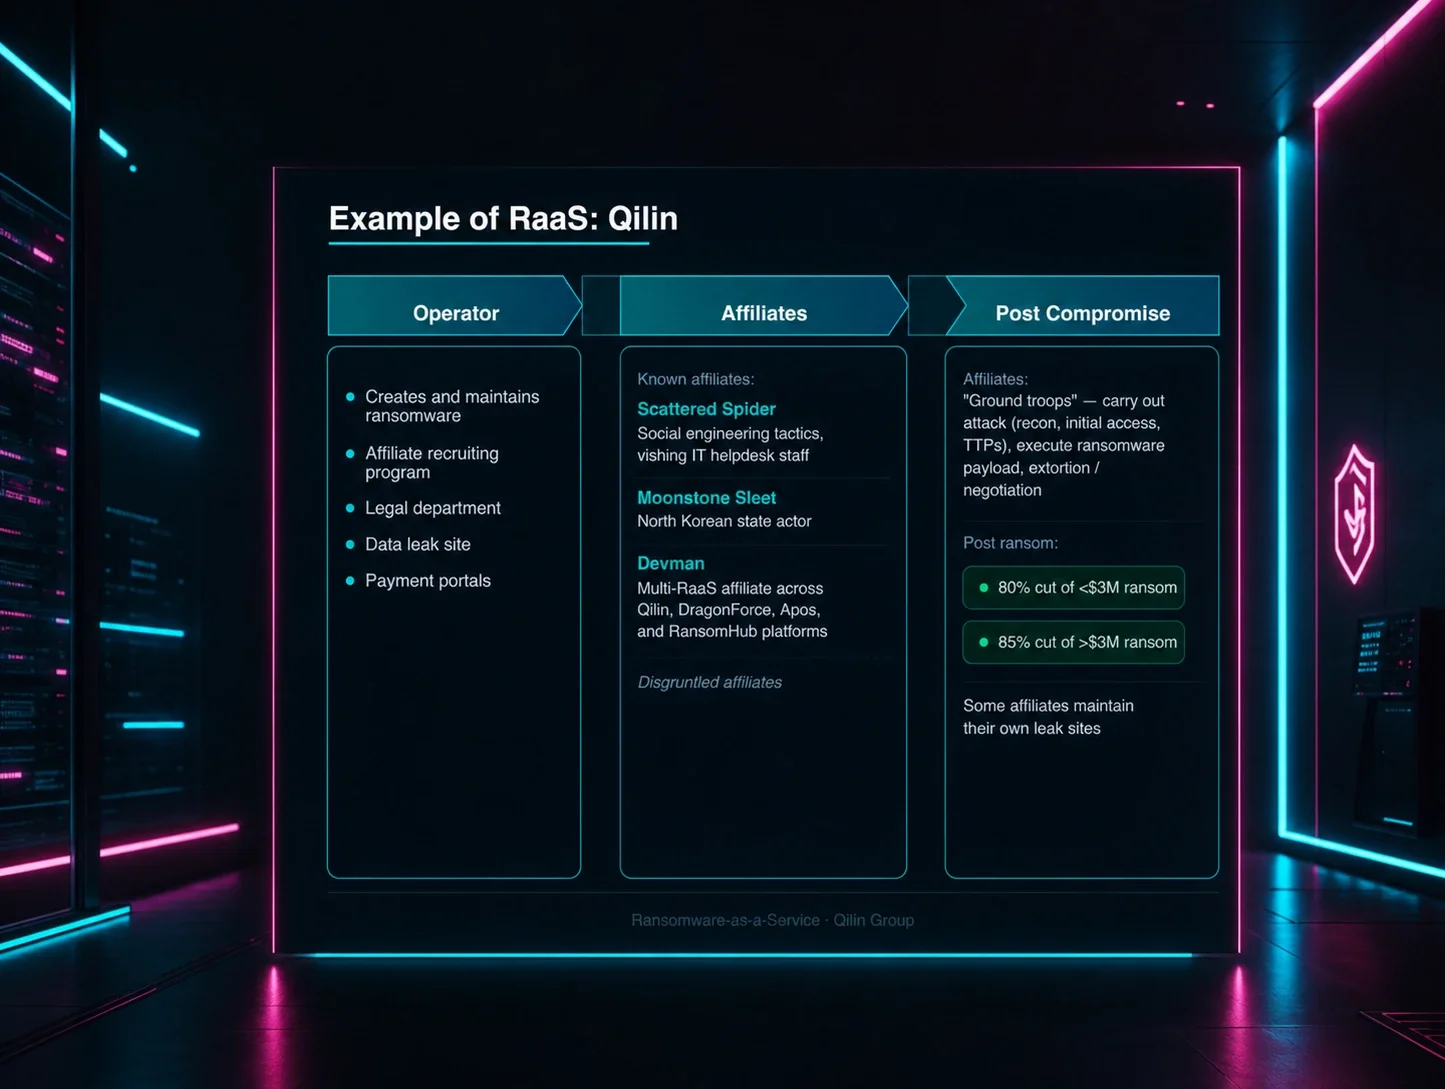
Huntress breaks down the ransomware-as-a-service (RaaS) ecosystem, explaining how operators (e.g., Qilin) provide the malware and infrastructure while diverse affiliates (Scattered Spider, Moonstone Sleet, Devman) handle intrusion, meaning the same ransomware brand can involve very different attack chains. It details real-world tradecraft: initial access via RDP abuse, vulnerable edge appliances like SonicWall VPNs (preceding Akira deployment), and rogue RMM tools (ScreenConnect, TeamViewer, Bomgar), plus persistence via hidden user accounts and RMMs like AnyDesk/Chrome Remote Desktop, defense evasion via EDR/AV killers and BYOVD, and exfiltration using 7-Zip, MegaSync, RClone, S5cmd, and finger.exe.
huntress.comwriteupAdded 3 Sep 2026, published 20 May 2026🛡️ Security - Threat Actors Weaponize Tiflux RMMs in Malspam Attacks
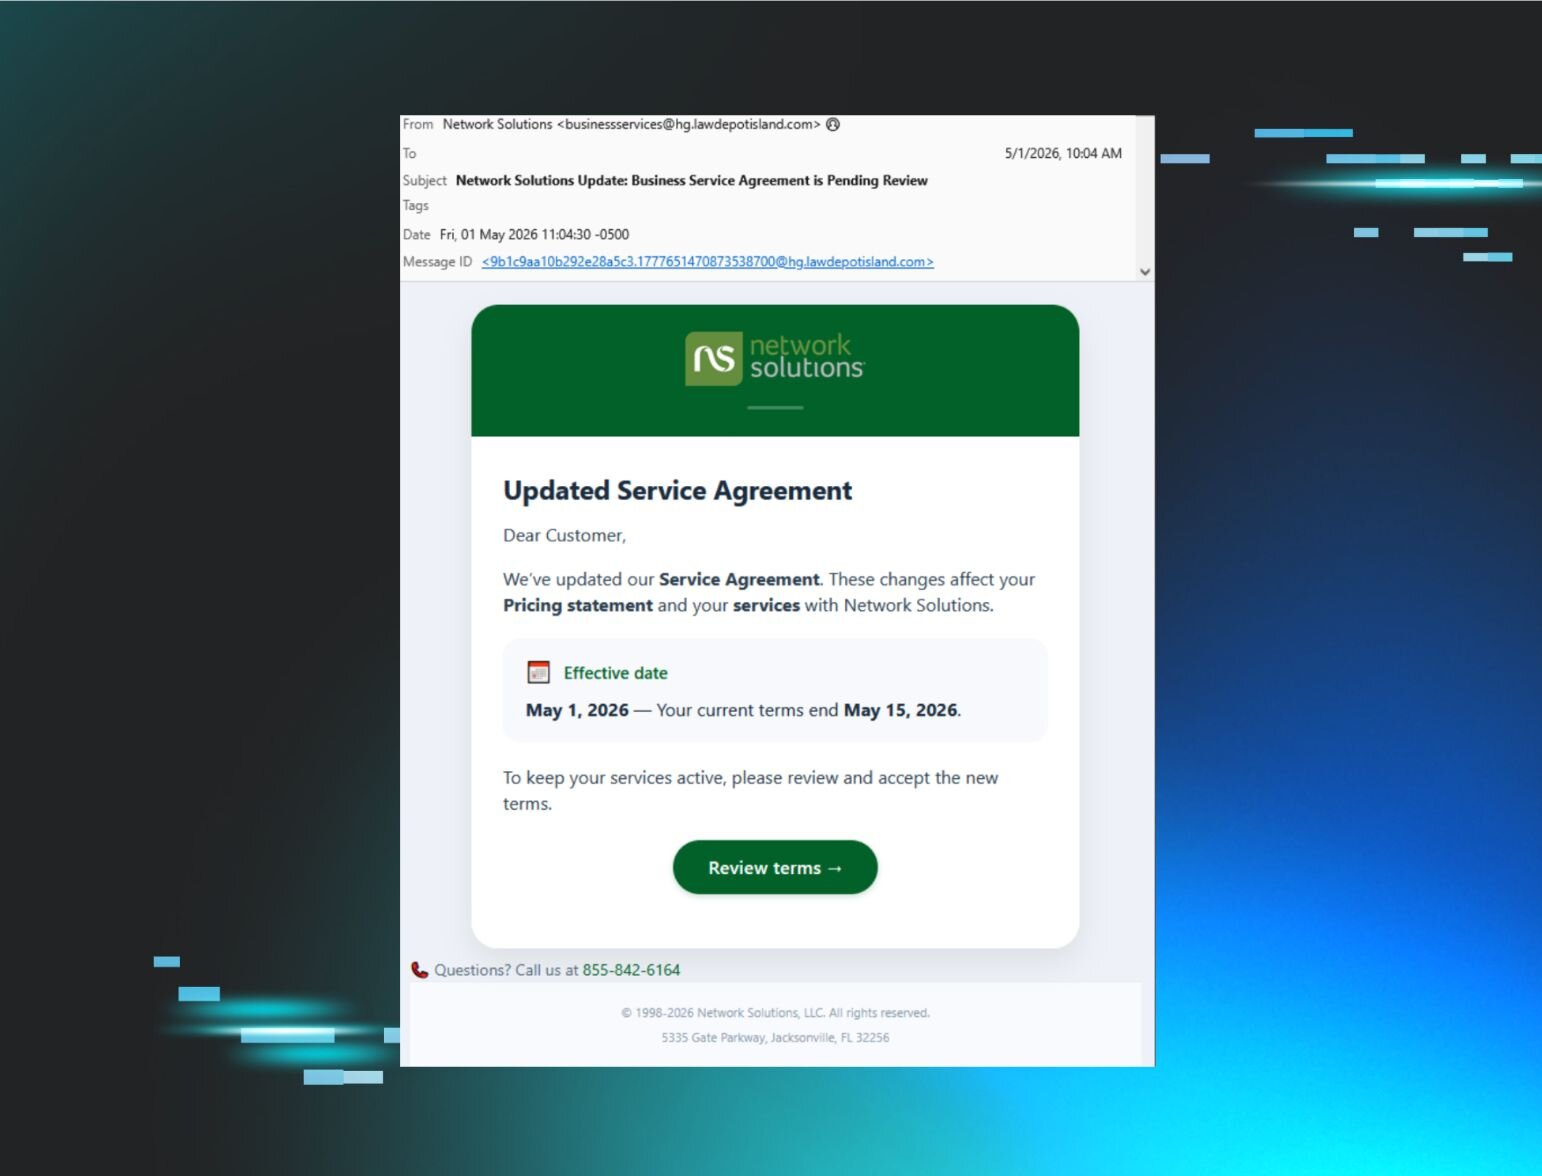
Huntress documents a malspam campaign, active since February 27, that uses fake "service agreement" document lures behind a CloudFlare CAPTCHA to trick targets into installing Tiflux, a lesser-known Brazil-based commercial RMM, before pivoting to UltraVNC, Splashtop, and ScreenConnect for persistent remote access. The Tiflux installer bundles suspicious extras beyond the legitimate agent: a decade-old UltraVNC build with hardcoded plaintext-recoverable passwords, an expired UltraVNC code-signing cert, registry files that stage a hidden TightVNC service (enabled even in Safe Mode) and a passwordless PuTTY SSH key to a peopleone[.]com[.]br server, registry tweaks that suppress Windows Secure Attention Sequence consent prompts, and a known vulnerable HwRwDrv.sys driver linked to privilege escalation with a revoked signing certificate. Huntress frames this as another entry in the ongoing "LOLRMM" pattern of attackers abusing legitimate commercial RMM tools for stealthy access and persistence.
huntress.comwriteupAdded 3 Sep 2026, published 7 May 2026🛡️ Security - Komari Red: The Monitoring Tool with a Built-in Reverse Shell
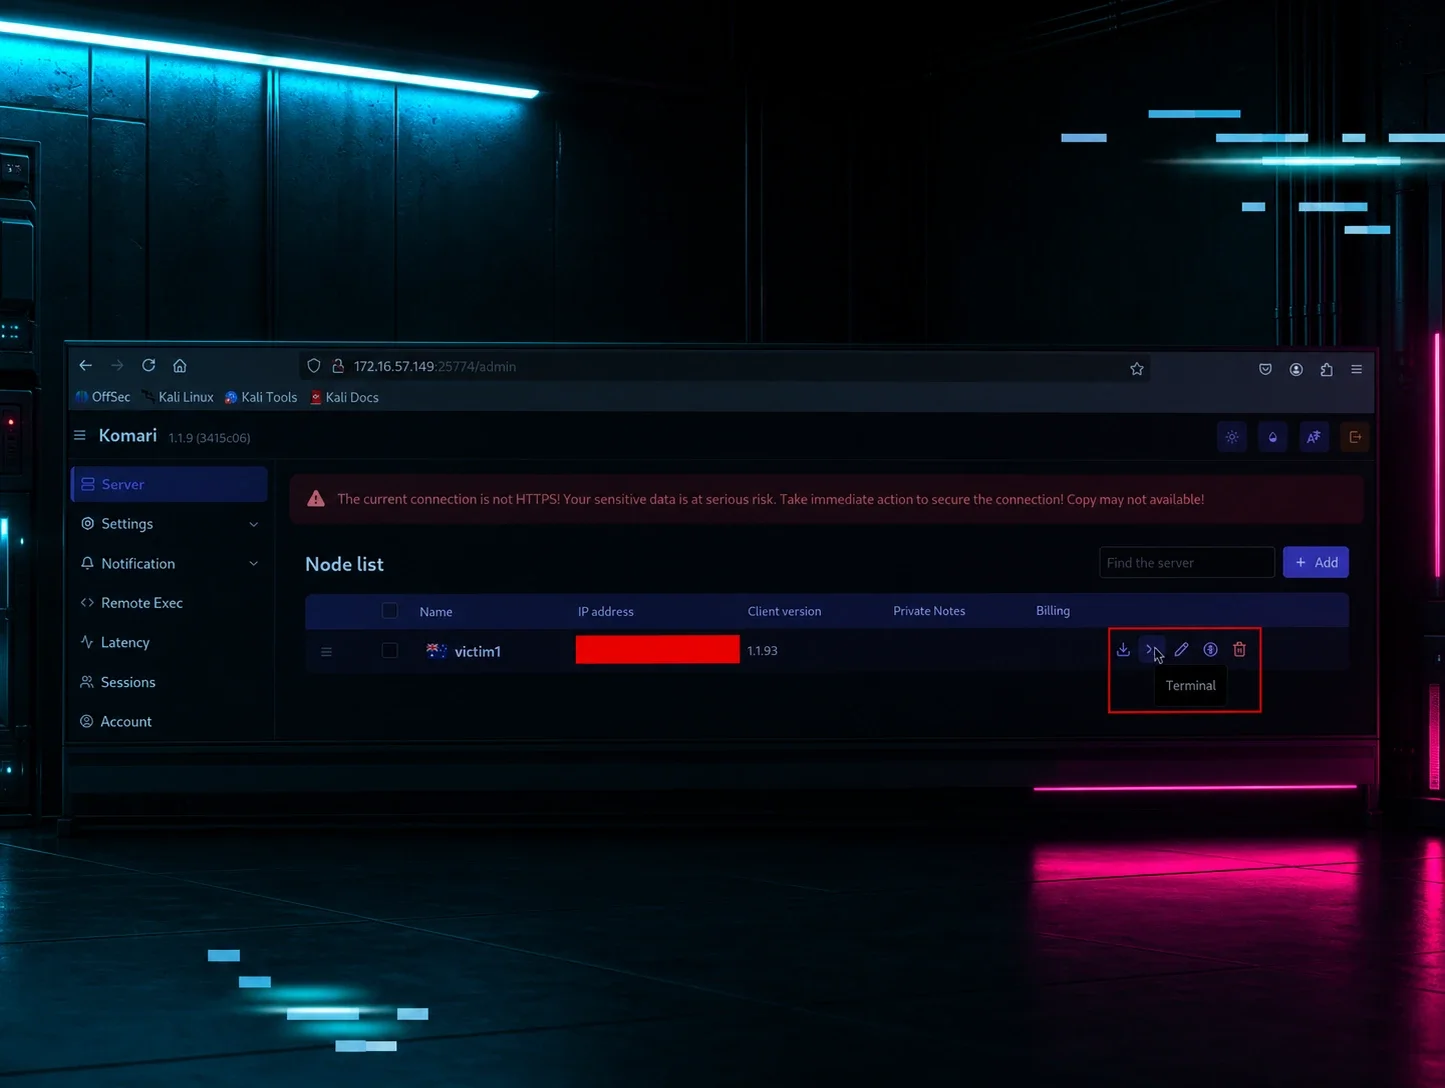
Huntress details a live intrusion where an attacker used stolen SSLVPN credentials, Impacket's smbexec.py (a customized fork with randomized artifact names) for lateral movement and registry-hive dumping, then enabled RDP via reg/netsh changes to interactively install the open-source "Komari" monitoring agent as a SYSTEM-level service named "Windows Update Service" via NSSM. Unlike other abused RMM/monitoring tools (Velociraptor, SimpleHelp, ScreenConnect, AnyDesk, Nezha, Atera), Komari ships arbitrary command exec, an interactive PTY reverse shell, and distributed ping/port-scanning enabled by default over a WebSocket that blends in as normal HTTPS traffic — turning a legitimate 4.3k-star GitHub monitoring tool into an out-of-the-box botnet-style C2 with no weaponization required.
huntress.comwriteupAdded 3 Sep 2026, published 30 Apr 2026🛡️ Security - Uptick in Bomgar RMM Exploitation
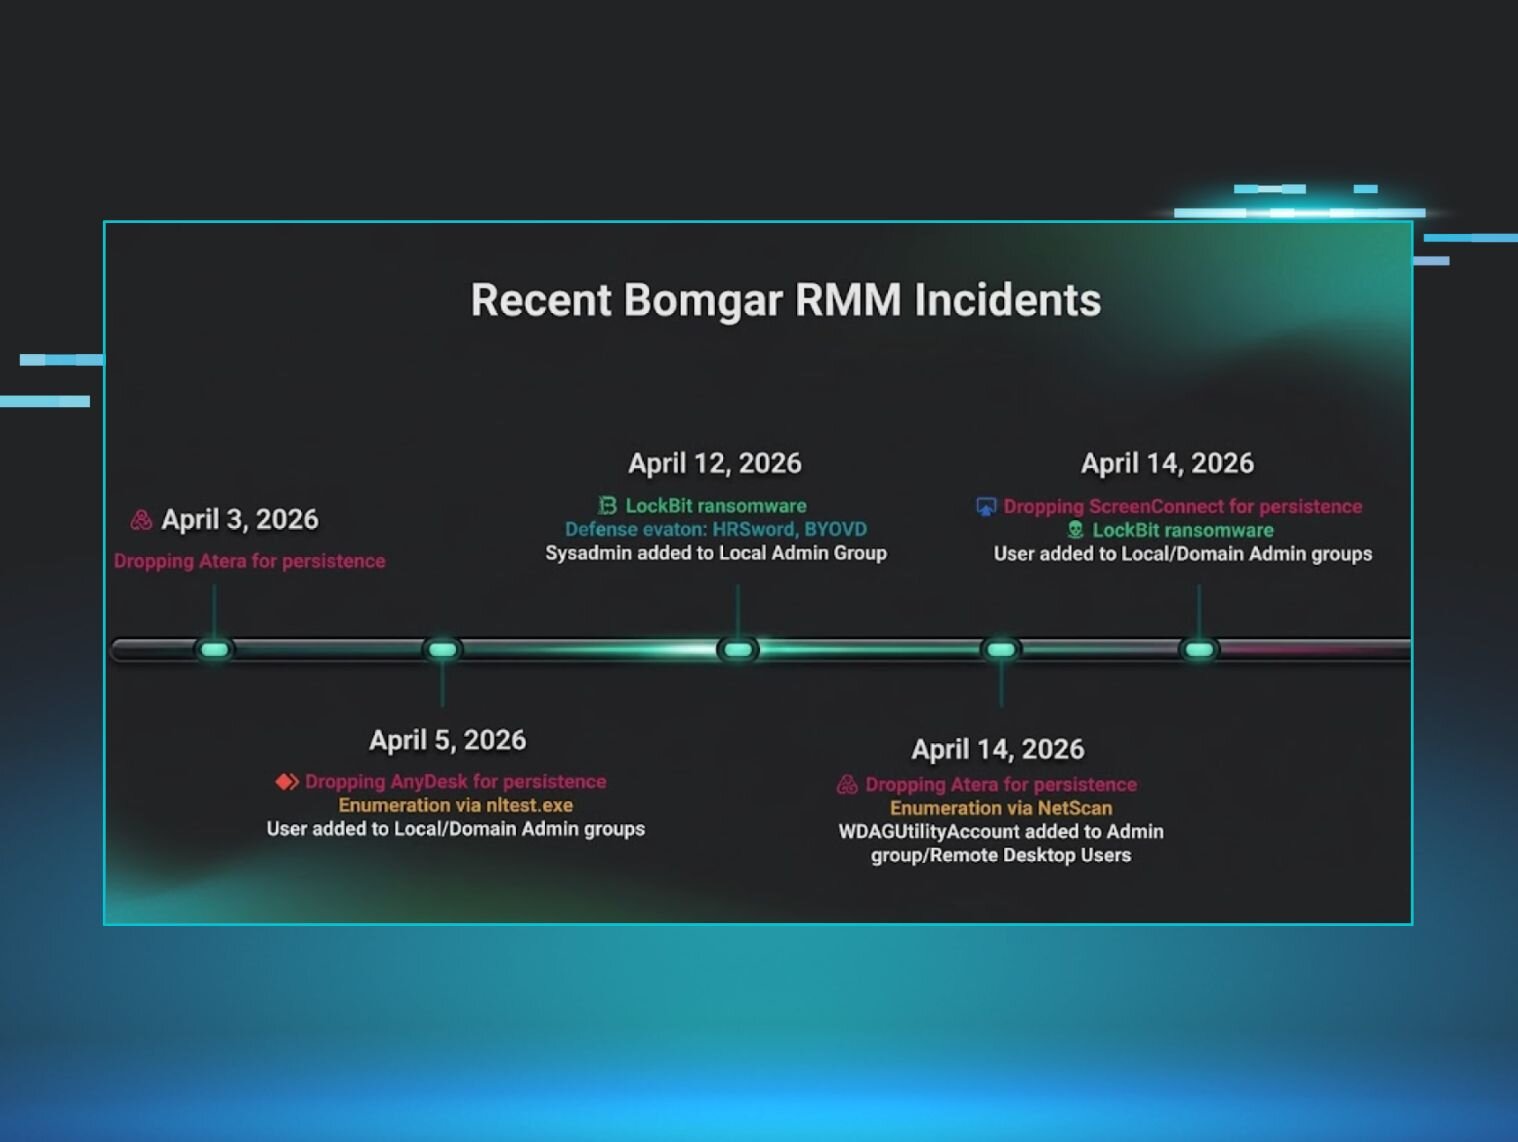
Huntress SOC documents an ongoing wave of exploitation of CVE-2026-1731, an unauthenticated RCE in Bomgar (rebranded BeyondTrust Remote Support/Privileged Remote Access), first disclosed in February 2026 and patched in versions 25.3.2/25.1. Attackers are using compromised outdated Bomgar instances — including at an MSP and a dental software vendor — to add rogue domain admin accounts, deploy LockBit ransomware (likely via a leaked LockBit 3.0 builder), drop the BYOVD EDR-killer PoisonKiller, and pivot to additional RMM tools like AnyDesk, Atera, ScreenConnect, and a renamed SimpleHelp for persistence across downstream customer environments.
huntress.comwriteupAdded 3 Sep 2026, published 17 Apr 2026🛡️ Security - Why the Stryker Attack Still Matters. And Five Steps You Can Take Today
Huntress analyzes the March 2026 Stryker incident, in which attackers linked to the pro-Iran group Handala reportedly compromised Stryker's Microsoft Intune/MDM environment and issued a mass 'Remote Wipe' command factory-resetting up to 200,000 corporate and BYOD devices, while also exfiltrating 50TB of R&D data. The piece explains why this 'weaponized remote wipe' differs from ransomware (no restore key, full rebuild required), details the supply-chain/patient-safety fallout for NHS orders, and gives five concrete defenses: locking down MDM/RMM/EDR consoles as crown-jewel assets, requiring multi-admin approval for bulk device actions, moving from MDM to MAM for BYOD, building out-of-band IR comms, and rehearsing a fleet-scale 'day zero' restore.
huntress.comarticleAdded 3 Sep 2026, published 8 Apr 2026🛡️ Security - How a Tax Search Leads to Kernel-Mode AV/EDR Kill
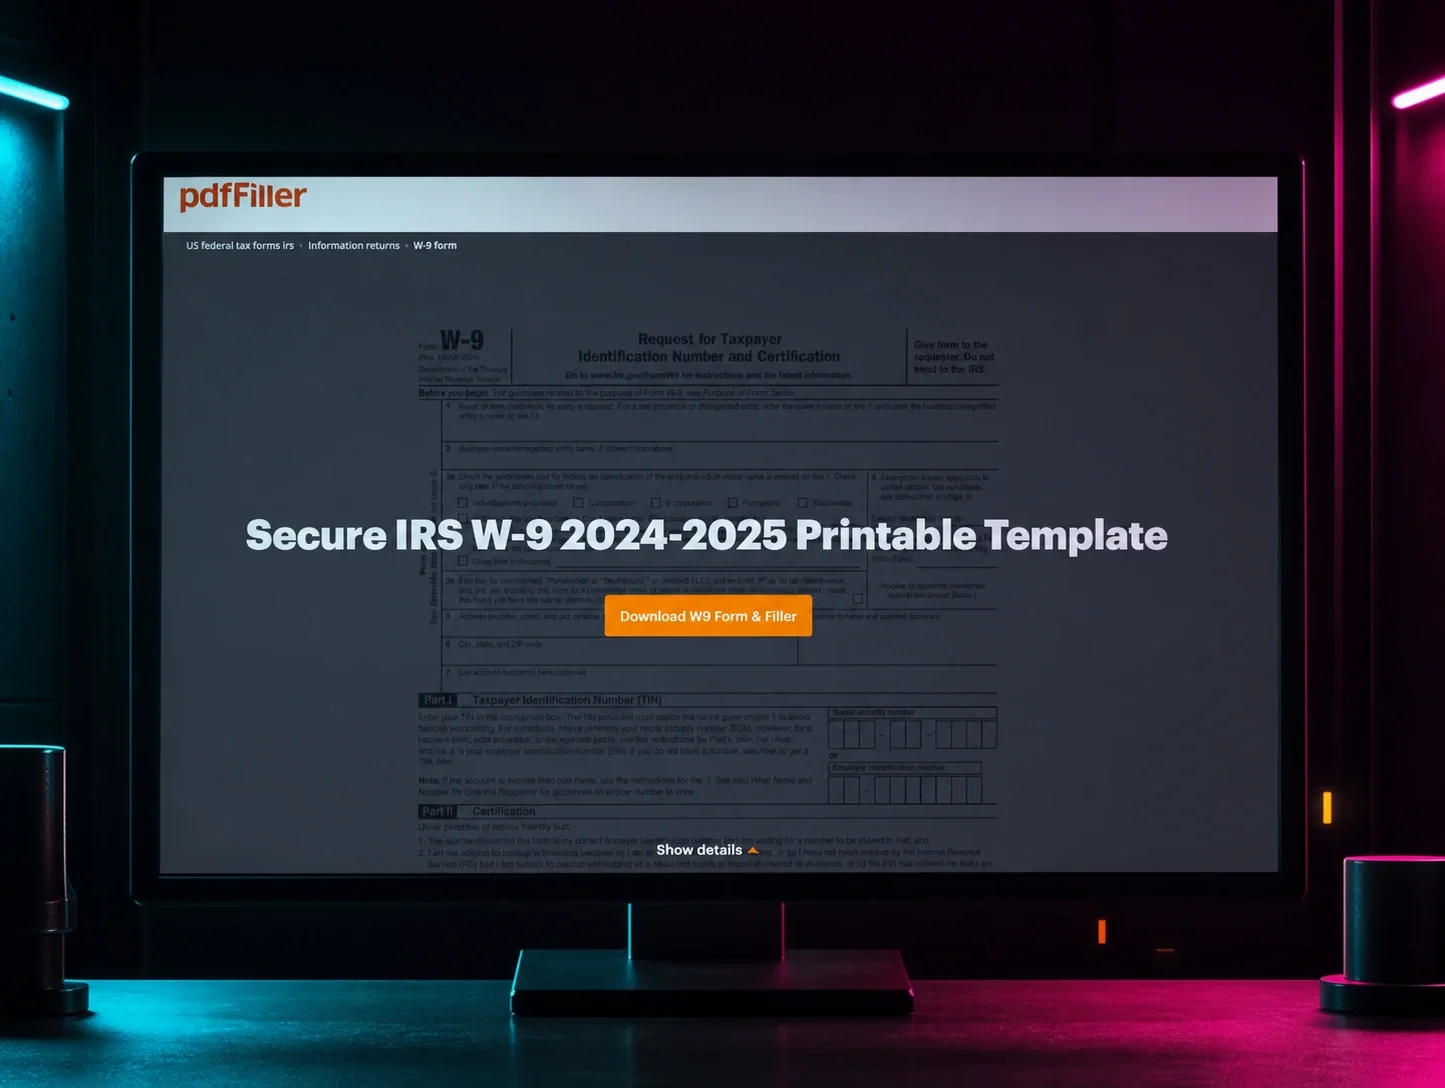
Huntress Tactical Response documents an active malvertising campaign (since Jan 2026) that uses Google Ads for tax-form searches (W-2/W-9) to deliver rogue ScreenConnect installers, leading to a BYOVD EDR killer that abuses a previously undocumented signed Huawei audio driver to terminate Defender, Kaspersky, and SentinelOne from kernel mode. The attack chain includes dual commercial cloaking services (JustCloakIt, Adspect) to evade researchers, a multi-stage crypter using a 2GB memory allocation trick to evade AV, stacked RMM tools (ScreenConnect, FleetDeck) for persistence, and post-EDR-kill LSASS dumping plus lateral credential harvesting via NetExec - consistent with a pre-ransomware/IAB playbook. The report also links a fake Chrome update page with Russian-language JS comments to the same operator's infrastructure.
huntress.comwriteupAdded 3 Sep 2026, published 19 Mar 2026🛡️ Security - How Threat Actors Abuse Remote Management Tools | Huntress
Huntress details how low-skill threat actors daisy-chain legitimate RMM tools (ScreenConnect, Action1, HeartbeatRM, AnyDesk, Atera, etc.) via invitation and Social Security themed lures, LLM-generated infostealer scripts, and multi-fallback browser download tricks hosted on GitHub repos (VH851, Drasticc) to gain and disguise persistent access. It also documents firsthand observation of an actor who signed up to Huntress itself, revealing their toolchain (DeepSeek, Email Extractor, Proxy SwitchyOmega, 9Proxy, CertifyTheWeb, Sordum Hide from Uninstall List, and a fake Windows Security PIN harvesting binary pin.exe) and victim data such as W-9 forms and SSNs collected via Telegram based exfiltration.
huntress.comwriteupAdded 3 Sep 2026, published 11 Mar 2026🛡️ Security - RMM Abuse: When IT Convenience Bites Back
Huntress breaks down the surge in Remote Monitoring and Management (RMM) tool abuse, citing a 277% jump in 2025 and finding that over 50% of suspicious Atera RMM activity cases tie back to ransomware. It walks through a real SOC incident where a threat actor used stolen RMM credentials to gain initial access to an MSP partner's environment, ran enumeration commands, and attempted to disable the Huntress agent before being contained within 12 minutes, and recommends shifting from trusting approved-tool presence to behavioral baselining and executable/endpoint fingerprinting of RMM software.
huntress.comarticleAdded 3 Sep 2026, published 5 Mar 2026🛡️ Security - Employee Monitoring and SimpleHelp Software Abused in | Huntress
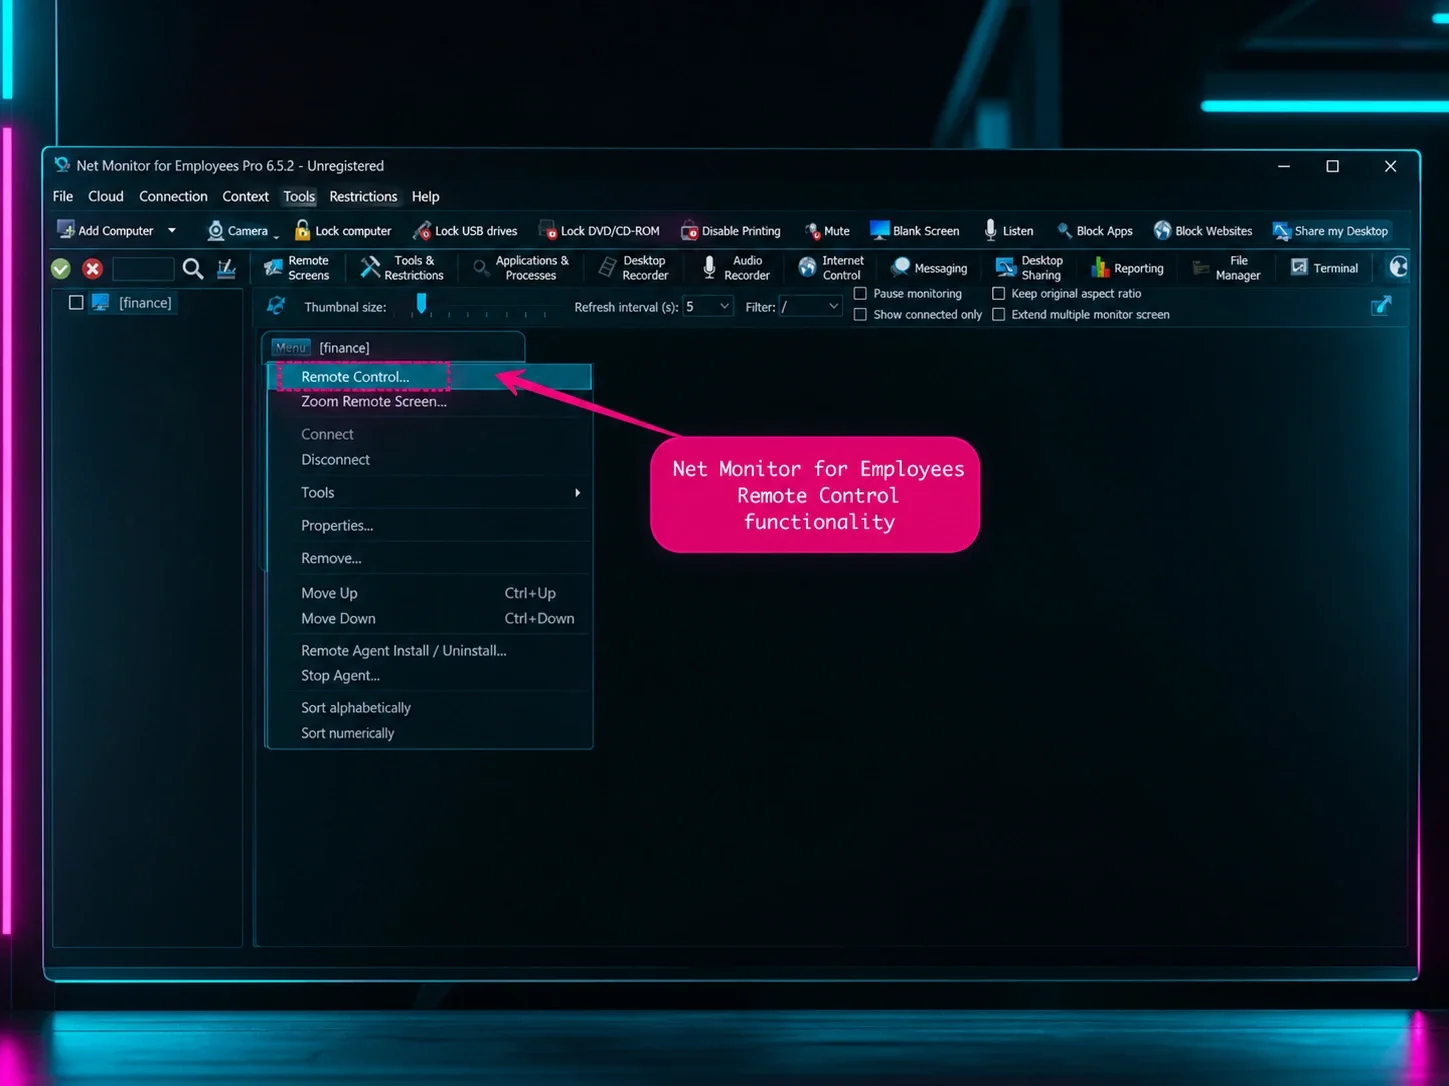
Huntress Tactical Response details two January-February 2026 intrusions where threat actors abused Net Monitor for Employees Professional (a commercial workforce-monitoring tool with a bundled pseudo-terminal, winpty-agent.exe) as a covert RAT, chained with a renamed SimpleHelp binary (vhost.exe) for redundant persistence. The attacker masqueraded the Net Monitor service as OneDrive (OneDriveSvc/svchost.exe), configured SimpleHelp with keyword triggers for cryptocurrency wallets/exchanges, and attempted to deploy Crazy ransomware (a VoidCrypt variant); shared infrastructure (dronemaker[.]org) and filenames across both cases point to a single operator. The writeup includes attack-chain timelines, IOCs, and hardening recommendations around MFA, RMM auditing, and process monitoring.
huntress.comwriteupAdded 3 Sep 2026, published 11 Feb 2026🛡️ Security



Showing 30 of 37
Show more