Skip to content

68 results for β€œPowerShell”

What you seeeverything
bleepingcomputer.comarticleπŸ›‘οΈ Security

Hugging Face malware campaign returns to hijack GPUs for crypto mining

A campaign of 31 malicious Hugging Face repositories across seven accounts, found by Pluto Security, posed as small Qwen2 checkpoints and used trust_remote_code to run a cryptominer and reverse shell on GPU inference hosts. The top model reached 28,412 downloads and scanned clean, and a second wave returned within days of takedown. The article also covers a fake Solana starter kit on GitHub that installs NetSupport Manager via a PowerShell one-liner aimed at AI coding agents.

Hugging FaceQwenXinference+3
Pluto SecurityAir Securitytrust_remote_code+9

Supply Chain, AI Security, Threat IntelΒ· Added 30 Oct 2026, published 29 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Node2Shell: Brotli Flaw Triggers Patching Across Microsoft, Node.js, Python Packages

CVE-2026-111497 (Node2Shell) is an out-of-bounds write in Google's Brotli decoder, versions 1.0.3 through 1.2.0, rated CVSS v4 9.2. Fixed in Brotli 1.0.10, 1.1.1 and 1.2.1, with patches from Node.js, Microsoft (.NET, Visual Studio, PowerShell on October 25), PyPI Brotli and brotlicffi, Bun, Envoy and Istio. Imperva showed code execution on Node.js 24.22.0 arm64; no in-the-wild exploitation is reported and some researchers say it only enables DoS.

BrotliNode.jsPython+3
CVE-2026-111497Node2ShellHTTP2Shell+5

AppSec, Supply ChainΒ· Published and added 26 Oct 2026

x.comthreadπŸ›‘οΈ Security

David Gutierrez | Eng (@david_x_ai) on X

Thread on a critical opencode bug disclosed by Pillar Security on Oct 19. On Windows and WSL, a remote MCP server could run code during OAuth sign-in, because the server-chosen authorization URL was put unescaped into a PowerShell command, so a PowerShell subexpression executed. opencode fixed it in 1.18.33 on Sep 28 as a browser-launch refactor with no advisory or CVE. MCP Inspector published an advisory for the same bug class, and its fix needs a major bump of the open package.

OpenCodeModel Context ProtocolPowerShell+3
Pillar Securitycommand injectionPowerShell subexpression+1

AI Security, AppSec, Supply ChainΒ· Added 27 Oct 2026, published 25 Oct 2026

dfir.chwriteupπŸ›‘οΈ Security

Field Notes: Reconstructing an Attacker’s Workflow

Field note from dfir.ch on PowerShell scripts an attacker left on disk during an incident: a file-watching command runner using Invoke-Expression, a fake Windows credential prompt that validates passwords via Start-Process and logs them in cleartext, AD computer enumeration with WMI access testing, and SMB share discovery via NetShareEnum. It notes where script labels overstate what they prove and lists hunting strings for Event IDs 4104, 4103, 4688 and Sysmon 1.

PowerShellActive DirectoryWMI+2
TerminalFixClickFixMicrosoft+7

Blue Team & Detection, Offensive SecurityΒ· Added 24 Oct 2026, published 22 Oct 2026

x.comthreadπŸ›‘οΈ Security

Santhosh Patel (@santhosh_patell) on X

Summary of Pillar Security research on opencode, in which a malicious remote MCP server runs code on a Windows or WSL machine during the OAuth login step. The login URL goes unsanitised into PowerShell through the npm "open" package, so an https:// link containing $(...) executes. Affected versions are 1.0.137 to 1.18.32, fixed in 1.18.33 (28 September) as a "refactor" with no advisory or CVE. The behaviour was first reported in 2020 as a WSL 2 broken-link bug.

OpenCodeModel Context ProtocolPowerShell+3
Pillar SecurityCWE-78silent fix

AI Security, AppSec, Supply ChainΒ· Added 21 Oct 2026, published 19 Oct 2026
securityweek.comarticleπŸ›‘οΈ Security

CikaBika Bot RAT Uses Discord for C&C

SecurityWeek reports Darktrace's findings on CikaBika Bot, a Rust-based RAT delivered via a PDF containing a disk image with an LNK disguised as a Word document. A hidden PowerShell step drops a Nim loader and a Rust DLL that is moved into the protected Edge directory to bypass UAC and sideloaded via DLL search-order hijacking of debugging-library exports. The RAT uses per-victim Discord channels for C&C (recon, command execution, file transfer, screenshots/camera) and exfiltrates ZIPped data via Ngrok.

RustNimDiscord+3
CikaBika BotDarktraceDLL search-order hijacking+3

Threat Intel, Malware & REΒ· Published and added 15 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Informer (@DarkWebInformer) on X

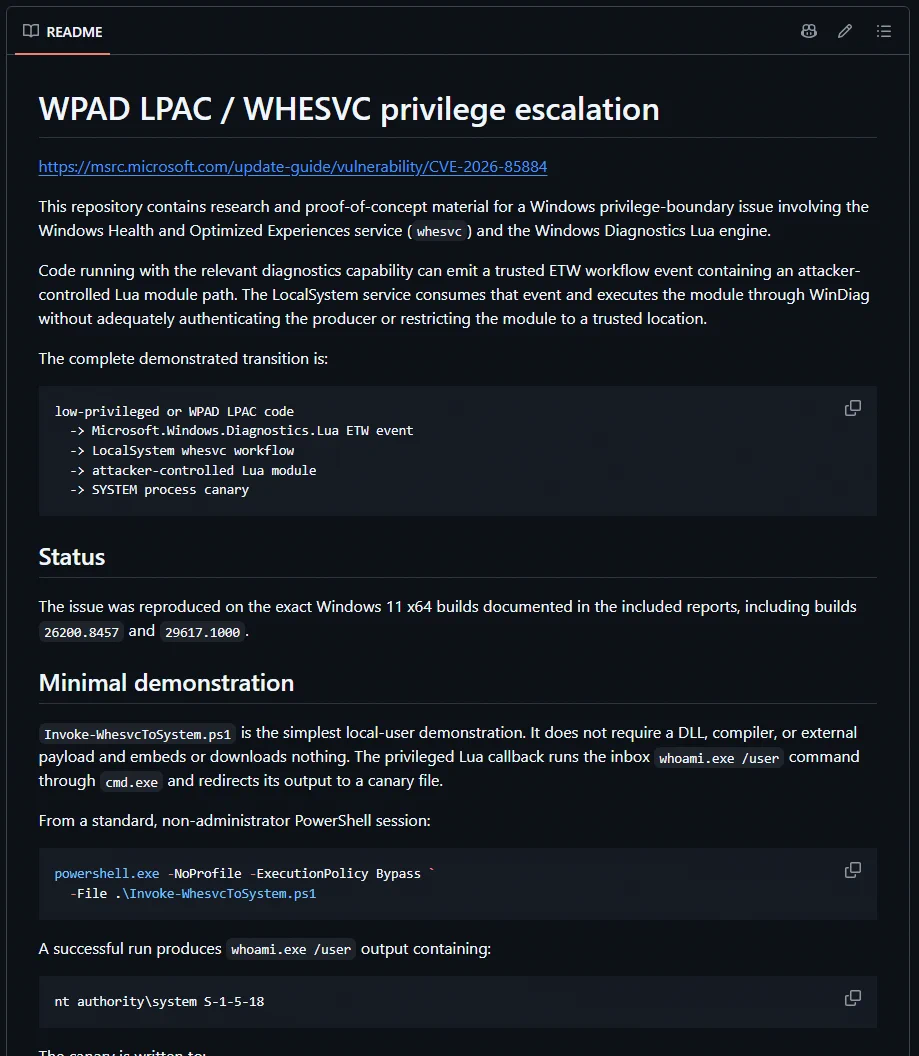
DarkWebInformer post on a PoC for CVE-2026-85884, a Windows 11 local privilege escalation in the Windows Health and Optimized Experiences service. Low-privileged code can trigger a trusted ETW event carrying an attacker-controlled Lua module path. The LocalSystem whesvc service then runs that module through WinDiag without validating the event producer or restricting the module location. The PoC takes a standard non-admin PowerShell session to NT AUTHORITY\SYSTEM on Windows 11 x64 builds including 26200.8457 and 29617.1000.

WindowsETWLua+1
CVE-2026-85884Windows Health and Optimized Experienceswhesvc+1

Offensive SecurityΒ· Added 15 Oct 2026, published 14 Oct 2026
blog.talosintelligence.comarticleπŸ›‘οΈ Security

Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations

Cisco Talos and Recorded Future Insikt Group describe UAT-6275 (TAG-193, overlapping Silent Lynx and YoroTrooper), a suspected Kazakhstan-nexus actor targeting CIS government, water and energy organizations. Exposed staging directories and a GitHub repo revealed four infection chains (macro documents, PS2EXE downloaders, GitHub-hosted PowerShell, and a WinRAR CVE-2025-8088 archive) delivering custom reverse shells Chvost, Laplas and PickleShell, plus Linux tooling and a FortiWeb CVE-2025-25257 PoC. The post includes victimology, a campaign timeline, attribution rationale (medium confidence), defender guidance and ClamAV/Snort coverage.

WinRARPowerShellGitHub+2
CVE-2025-8088CVE-2025-25257UAT-6275+13

Threat Intel, Malware & REΒ· Published and added 14 Oct 2026
dfir.chwriteupπŸ›‘οΈ Security

Field Notes: EtherRAT Distributed Through a Legitimate Intune Workflow

DFIR case where a malicious MSI impersonating Advanced IP Scanner, sourced from a fake GitHub repo found via Bing, was imported by a customer into Microsoft Intune and deployed to four endpoints, running a Node.js-based EtherRAT chain. It traces the infections by correlating the MSI ProductCode, MDMAppInstaller/omadmclient process ancestry and Intune app inventory (Graph PowerShell query). It also covers renamed node.exe hash-hunting pitfalls, Ethereum RPC dead-drop C2 traffic, a screen-capture script and a second impersonating repo.

Microsoft IntuneNode.jsEthereum+3
EtherRATEtherHidingAtos Threat Research Center+4

Blue Team & Detection, Threat Intel, Malware & REΒ· Added 14 Oct 2026, published 13 Oct 2026

x.comthreadπŸ›‘οΈ Security

Ned Peterson (@NedPeterson99) on X

A post summarizing a joint FBI and six-country advisory on actors tied to Integrity Technology Group (the sanctioned Chinese firm linked to Flax Typhoon and the Raptor Train botnet). They password-sprayed Microsoft 365 and Exchange accounts over EWS, OWA, ActiveSync and PowerShell with EBurst. They then drained mailboxes with a PHP bot over Exchange Web Services and an office-cli utility using stored client ID, tenant ID and secret values, and exposed the stolen email to third parties through a web app, in some cases restricted to Xiamen IP addresses. Victims were in government, law enforcement, healthcare and religious organizations across Southeast Asia, Africa and North America, with activity since at least January 2021. Defensive takeaways: enforce MFA on every legacy path, retire basic auth and EWS, audit OAuth apps and service principals with mail-read rights, and alert on bulk mailbox pulls.

Microsoft 365Microsoft ExchangeEBurst+3
Integrity Technology GroupFlax TyphoonRaptor Train+3

Threat Intel, Identity & AccessΒ· Added 11 Oct 2026, published 9 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

Threat Actors Exploit Critical AhsayCBS Flaws to Drop Webshells and XMRig Cryptominer

Huntress documents active exploitation of two AhsayCBS (Ahsay Cloud Backup Server) vulnerabilities being chained together: CVE-2026-105133, an authentication bypass in checkSysPwd, and CVE-2026-105134, an unauthenticated RCE in the Replication Receiver's UpdateReceivers.do endpoint that grants SYSTEM. Attackers use the chain to drop JSP webshells, then deploy a renamed XMRig cryptominer (masquerading as msedge.exe via a modified NSSM binary), a Task-Manager-aware anti-detection PowerShell script, and the vulnerable WinRing0x64.sys kernel driver for hardware-level miner access. Huntress provides IOCs, mitigation guidance (restrict management interface, re-image if compromised) and four Sigma rules targeting each stage of the intrusion chain.

AhsayCBSXMRigSigma+3
CVE-2026-105133CVE-2026-105134WinRing0x64.sys+2

Threat Intel, Blue Team & Detection, AppSecΒ· Added 9 Oct 2026, published 8 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue RMMs

Huntress details a phishing campaign that abuses legitimate Microsoft Power BI dashboards (app.powerbi.com) to host a fake "Download Reference" lure that bypasses mail filters trusting the Microsoft domain. Clicking the lure triggers browser/environment fingerprinting and Telegram-bot-based victim telemetry exfiltration via attacker domains (dailylifeproject.site, burnsworth.site, etc.), then silently downloads rogue ScreenConnect installers; a chained CMD/PowerShell script (SCAutoFix.ps1) deploys a second ScreenConnect instance, uninstalls the first for evasion, drops the defense-evasion tool HideUL_x64.exe, and sets a recurring scheduled task before Huntress's SOC intervened.

Power BIScreenConnectTelegram+3
HideUL_x64.exeSCAutoFix.ps1SCAutoRepairEvery2Min

Threat Intel, Blue Team & DetectionΒ· Published and added 7 Oct 2026
huntress.comwriteupπŸ›‘οΈ Security

Up a Creek Without a Command Line: Mapping an Akira Ransomware Attack | Huntress

Huntress researchers reconstruct an Akira ransomware attack timeline using forensic artifacts collected after the Huntress agent was installed post-compromise, including Windows Registry Shellbags, Event Logs, and Akira ransomware log files. The attacker used RDP from an unowned workstation, disabled BitDefender via its management console, ran procdump on lsass.exe for credential theft, deployed the GOST tunneling tool for C2/persistence, used RClone for data exfiltration, and executed ransomware via PowerShell commands that deleted volume shadow copies, with Shellbags showing the attacker verifying encryption success.

PowerShellWindowsEDR+2
AkiraUNC5330BitDefender+1

Threat Intel, Blue Team & DetectionΒ· Published and added 6 Oct 2026

unit42.paloaltonetworks.comarticleπŸ›‘οΈ Security

Blinder Tunnel Campaign Targets Iraqi Infrastructure

Unit 42 details "Blinder Tunnel," a campaign by Iranian state-aligned actor CL-STA-1178 (linked to Elastic's "The Shelby Strategy") that impersonated Dubai Airports recruiters to deliver a trojanized Visual Studio coding-challenge archive against an Iraqi critical-infrastructure target, with related activity against UAE aviation and Israeli entities via Google Drive-themed phishing. The report dissects a three-stage infection chain (weaponized .csproj MSBuild target abuse, AppDomainManager hijacking to disable ETW, and DLL sideloading into RuntimeBroker.exe) that deploys ShelbyLoader V2, the ShelbyC2 V2 RAT, PsProxy.dll (in-memory PowerShell execution), and Blackwood, a custom Chisel-based tunneling loader; C2 abuses GitHub's API and GitHub Issues as a dead-drop fallback, and attribution rests on an Iranian-hosted IP, Persian-domain infrastructure overlap, and MP3 metadata pointing to MusicDel.ir. Includes full IOCs (hashes, IPs, phishing domains, registry keys).

GitHub.NETPowerShell+3
CL-STA-1178ShelbyLoader V2ShelbyC2 V2+16

Threat Intel, Malware & REΒ· Published and added 6 Oct 2026

github.comrepo🧠 AI

Zhenyu98/codex-chatgpt-bridge

codex-chatgpt-bridge is a Codex agent skill plus external PowerShell control scripts (On/Off/Reboot/Rotate) built on top of the open-source DevSpace MCP bridge, which lets ChatGPT act as a planning/review "architect" while Codex stays the local executor that applies and verifies changes. It adds a token-saving router (NORMAL / TOKEN_SAVING / CHATGPT_ARCHITECT modes) and a lifecycle layer β€” Cloudflare Quick Tunnels or a stable Cloudflare Worker proxy, DPAPI-protected credentials, OAuth token rotation, and a scheduled-task recovery entrypoint β€” so the bridge's public endpoint can be closed when idle without re-authorizing the ChatGPT app on every restart.

Model Context ProtocolCodexChatGPT+5

coding-agents, mcpΒ· Added 5 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

The First 24 Hours: What Happens When Ransomware Lands

An hour-by-hour ransomware incident response playbook written by UnderDefense CEO Nazar Tymoshyk and published on Huntress's blog, covering confirmation, containment, exfiltration detection, backup/recovery pitfalls, and root-cause investigation in the first 24 hours of an attack. It draws on Mandiant's M-Trends 2026 report (14-day median dwell time, 22-second access-broker-to-ransomware handoff) and CISA's November 2025 Akira advisory (VPN without MFA as primary access vector, exfiltration via FileZilla, WinRAR, WinSCP, RClone, Mega and Ngrok, credential dumping with Mimikatz and LaZagne, PowerShell-based shadow copy deletion) alongside real UnderDefense engagement anecdotes.

PowerShellMimikatzCobalt Strike+2
AkiraMandiant M-Trends 2026REDBIKE+6

Blue Team & Detection, Threat IntelΒ· Added 3 Oct 2026, published 2 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

Defender Exclusion Abuse: How Attackers Hide Malware from MDAV

Huntress breaks down how Microsoft Defender Antivirus (MDAV) path/extension exclusions can be abused to hide malicious binaries from scans, detailing the registry internals (HKLM...Windows Defender\Exclusions vs the GPO-driven Policies key) and the four ways to set them: PowerShell (Set/Add-MpPreference), the MSFT_MpPreference WMI class, GPO, and direct registry edits. It documents real-world abuse by GootKit (2019), WhisperGate (2022), and Muddled Libra (2024), plus an under-documented trick where setting HideExclusionsFromLocalAdmins blocks even SYSTEM from querying exclusions via PowerShell/WMI, and describes the registry-level telemetry and detections Huntress built to catch both behaviors.

Windows DefenderPowerShellWMI+1
GootKitWhisperGateMuddled Libra+1

Blue Team & Detection, Offensive SecurityΒ· Added 1 Oct 2026, published 30 Sep 2026

blog.talosintelligence.comwriteupπŸ›‘οΈ Security

China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor

Cisco Talos details UAT-11587, a China-nexus threat cluster targeting government, defense, and policy organizations across Taiwan, India, the Philippines, Cambodia, and other Asian countries with spear-phishing and a five-stage infection chain (HTA/WSF stagers, JScript decryptors, .NET BinaryFormatter/ActivitySurrogateSelector deserialization gadgets, and DLL sideloading via the signed GatherOsState.exe) to deploy a new Rust-compiled backdoor called Antino. Antino uses Microsoft Graph/Outlook/OneDrive as a dead-drop C2 channel instead of a traditional C2 server, supports shell/PowerShell execution, file transfer, shellcode loading with a sleep-mask evasion technique, and abuses the Windows Scripted Diagnostics framework for persistence; Talos also notes possible infrastructure overlap with Symantec's "Jewelbug" cluster and Arctic Wolf's UNC6384 reporting. Includes ClamAV/Snort coverage and IOCs.

RustMicrosoft 365PowerShell+4
UAT-11587AntinoJewelbug+5

Threat Intel, Malware & REΒ· Added 7 Oct 2026, published 30 Sep 2026

huntress.comwriteupπŸ›‘οΈ Security

Determined Attacker Uploads Malicious Webshells to Parks and Rec Management Platform Servers

Huntress details a four-act intrusion against a shared parks-and-recreation management platform running on IIS, where an attacker first tried noisy unauthenticated exploits (IIS 8.3 tilde enumeration, WebDAV verb abuse, upload-handler bypasses) before simply registering a member account and uploading .aspx webshells via a member-file upload feature across three servers. The attacker enumerated hosts, extracted web.config/connection strings, hunted for cardholder data (Fortis/MXMerchant webhook logs, CVV/card-number strings), then escalated to timestomping, re-deploying known-filename webshells, and finally injecting an AI-generated PowerShell/JS dropper into a trojanized jQuery file to turn site visitors' browsers into WebRTC/WebSocket C2 clients (ririmochii/bubuneeko Cloudflare Workers infrastructure). Includes a zh-CN PowerShell user-agent string used for attribution and full command/IOC listings useful for detection engineering.

IISPowerShellWindows+3
ririmochii[.]workers[.]devbubuneeko[.]workers[.]devIIS 8.3 tilde enumeration+2

Threat Intel, Blue Team & Detection, Offensive SecurityΒ· Added 1 Oct 2026, published 30 Sep 2026

microsoft.comwriteupπŸ›‘οΈ Security

Phishing Abuses RMM Tools for Persistent Access

Microsoft Defender Experts document a July 2026 phishing campaign that delivers a masqueraded but legitimately signed MSP360 RMM installer (v2.5.0.67) via meeting-invite, Zoom, Adobe, and DHL-themed lures hosted on both attacker infrastructure and legitimate cloud services (S3, Cloudflare R2, Dropbox, GitLab, Supabase). After UAC-elevated installation and service persistence, the RMM.Agent.exe service launches PowerShell to silently install a ConnectWise ScreenConnect client via msiexec, which the actor then uses via RunFile to drop credential-theft and reconnaissance tools disguised as Windows/Defender/Phone Link components. A separate July intrusion used FaronicsDeployAgent.exe the same way to deploy ScreenConnect, showing the technique is not MSP360-specific; Microsoft provides IOCs, hunting queries, and mitigation guidance (Application Control, AppLocker publisher rules, ASR rules) but does not attribute the activity.

MSP360ScreenConnectPowerShell+3
T1583.001T1583.006T1566.002+16

Threat Intel, Blue Team & DetectionΒ· Added 7 Oct 2026, published 29 Sep 2026

huntress.comwriteupπŸ›‘οΈ Security

Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix

Huntress researchers document a campaign where attackers built a malicious ChatGPT Custom GPT ("Plus 5.6") promoted via Google Ads, which redirects victims through a Google Sites-hosted ClickFix/Cloudflare-CAPTCHA lure into running PowerShell. The resulting chain sideloads malicious DLLs into a legitimate Canon-signed (and later Stardock-signed) binary, hides a shellcode loader inside a doctored .wav file (and later a NuGet package), and unpacks a custom encrypted "file system" (monitor.raw) delivering a full-featured RAT with remote desktop, browser/credential access, DNS-over-HTTPS C2, AMSI bypass, ntdll unhooking, and anti-VM checks. Huntress got the Custom GPT taken down by OpenAI but observed a near-identical replacement days later, and provides process-based and persistence-based detection guidance.

ChatGPTPowerShellWindows+3
ClickFixAMOS stealerMacSync+9

Threat Intel, Malware & RE, AI SecurityΒ· Added 29 Sep 2026, published 28 Sep 2026

huntress.comwriteupπŸ›‘οΈ Security

The Not So Silent Miner: Threat Actor Compiles Cryptominer on the Endpoint

Huntress SOC analyzes an intrusion that began with exploitation of Samsung MagicINFO (CVE-2025-4632, after incomplete fix of CVE-2024-7399) via tomcat9.exe. The actor took three tries to install AnyDesk (certutil and PowerShell attempts were blocked by Defender), created an 'oldadministrator' account, disabled Defender, then ran Silent XMR Miner Builder, which compiled a Monero miner on the endpoint using csc.exe, cvtres.exe, donut, tcc and MinGW gcc. The miner ran masquerading as explorer.exe against C3Pool; the post gives command lines and detection ideas such as unusual compiler child processes from an unsigned parent and explorer.exe with mining arguments.

Samsung MagicINFOAnyDeskWindows Defender+3
CVE-2025-4632CVE-2024-7399SilentXMRMiner+10

Blue Team & Detection, Threat IntelΒ· Published and added 24 Sep 2026

huntress.comwriteupπŸ›‘οΈ Security

Google Doc Sidebar Sends Mac and Windows Users Down Different Paths to Malware

Huntress SOC analysts Ryan Dowd and Jon Semon tore apart a live social-engineering campaign that began with a fake CoinDesk marketing exec DMing a researcher a Google Doc containing a container-bound Apps Script sidebar. The script ran client-side without OAuth consent, exfiltrated victim IP/geolocation/wallet presence via the Telegram API, then routed macOS users to a piped zsh/DMG AMOS stealer chain and Windows users through ClickOnce and PowerShell loaders using three stolen or fraudulent code-signing certificates (a Norwegian company, Discord, and Lenovo). The Windows chain culminated in NetSupport Manager RMM abuse, a Ledger wallet implant, and a self-generated rogue root certificate authority (spoofing Google Trust Services) installed via MsBuild.exe hollowing to silently intercept HTTPS traffic, which the authors flag as the artifact most likely to survive incident remediation short of full reimaging.

WindowsmacOSGoogle Workspace+3
AMOS stealerClickFixMacSync+6

Threat Intel, Malware & REΒ· Added 11 Sep 2026, published 15 Sep 2026

github.comrepoπŸ›‘οΈ Security

KillaBoi/BrokenPipe

BrokenPipe is a PowerShell PoC that escalates a standard Windows user to NT AUTHORITY\SYSTEM by abusing the Steam Client Service (steamservice.exe). It connects to the service's shared-memory IPC, whitelists a genuine Valve-signed install-script VDF against a caller-controlled installation root (IClientInstallUtils::AddInstallScriptToWhiteList), then triggers RunInstallScript so the SYSTEM service launches a relocated executable (by default cmd.exe) without any UAC prompt. The flaw was reported to Valve in March and remained unpatched as of the write-up, validated on Steam 10.96.30.42 on Windows 10/11 x64.

PowerShellWindowsSteam
John HammondIClientInstallUtils::AddInstallScriptToWhiteListIClientInstallUtils::RunInstallScript

Offensive SecurityΒ· Added 2 Oct 2026, published 14 Sep 2026

blog.talosintelligence.comwriteupπŸ›‘οΈ Security

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager

Cisco Talos reconstructs two related WebDAV-based infection chains (tracked actor UAT-10820) that use a ClickFix fake-CAPTCHA lure, EtherHiding on BNB Smart Chain to stage JavaScript via a malicious Cloudflare Worker, and WebDAV-delivered disguised DLLs executed via rundll32 ordinal calls to drop the Amatera stealer. Depending on the C2 configuration, Amatera then deploys either a NativeAOT-loaded ZigCryptoStealer with a BYOVD EDR-killer driver and a Go-based Yamux reverse proxy, or a PowerShell stager that installs a trojanized NetSupport Manager RAT pointed at Russian C2 infrastructure. The post details loader internals, Amatera's dead-drop C2 resolution via Telegraph and Steam, and provides ClamAV signatures plus a full IOC list.

WebDAVPowerShellGo+3
UAT-10820AmateraZigCryptoStealer+8

Threat Intel, Malware & RE, BlockchainΒ· Added 7 Oct 2026, published 8 Sep 2026

huntress.comwriteupπŸ›‘οΈ Security

Daisy-Chaining Trust: Investigating Faronics Deploy Abuse | Huntress

Huntress details a phishing campaign that tricks victims into installing a legitimately signed Faronics Deploy agent disguised as Adobe/Zoom documents, enrolling endpoints into an attacker-controlled deployment console. The threat actors then abuse Faronics' remote script execution to pull PowerShell payloads (via curl, mshta, msiexec) from GitHub-hosted staging and install ScreenConnect for persistent remote access. The post identifies key forensic artifacts (C:\ProgramData\Faronics\Logs\ScriptRunner.log and the deployment's unique "ck" identifier) that defenders can use to trace attacker infrastructure and cluster malicious enrollments, and notes Faronics' response to disrupt abuse after Huntress's disclosure.

Faronics DeployScreenConnectPowerShell+2
ScriptRunner.logck identifierfileportals.gytgtecg[.]xyz

Threat Intel, Blue Team & DetectionΒ· Added 5 Sep 2026, published 31 Aug 2026

opensourcemalware.comtalkπŸ›‘οΈ Security

The OpenSourceMalware Show #18

Episode 18 of the OpenSourceMalware Show discusses the compromise of Rust maintainer 'dhrundy' that pushed malicious versions of arrayref (245M+ downloads), internment, and append-only-vec with a typosquatted build dependency executing a remote binary at compile time, which Wiz Research ties to DPRK infrastructure shared with the Mastra and Axios npm compromises. It also covers StubMaker, a campaign that started as RubyGems typosquats of bundler/i18n/rake/activesupport and shares byte-identical payloads (a 22MB Rust loader with an embedded Go infostealer, including a Chrome App-Bound Encryption bypass) with a 40-package npm typosquatting cluster targeting axios, chalk, commander, lodash, react and typescript, with signs it also hit PowerShell. The hosts also note a rising trend of attackers bundling compiled C++/Rust/Go binaries in npm/RubyGems packages (a red flag for analysts) and a PolinRider reinfection wave now using NullReceiver instead of EtherHiding for stage-two C2 hiding.

RustnpmRubyGems+3
StubMakerarrayrefDPRK+9

Supply Chain, Threat Intel, Malware & REΒ· Added 3 Sep 2026, published 21 Aug 2026

huntress.comwriteupπŸ›‘οΈ Security

Bank of America Phishing Email Delivers ScreenConnect Malware

Huntress dissects a Bank of America-themed phishing email that lures victims into downloading AccountGuardSetup.vbs, which unpacks through several layers of base64-encoded PowerShell to silently install ScreenConnect RMM with Administrator privileges. The chain uses AES-128-CBC encrypted blobs to deliver a C# UAC-bypass exploit via the ICMLuaUtil COM interface (MITRE ATT&CK T1548.002), then hides the resulting ScreenConnect service (renamed "Windows Security") from users and admins using SDDL/ACL manipulation so it can't be seen, logged, or removed.

ScreenConnectPowerShellWindows+2
T1548.002ICMLuaUtilBank of America phishing

Threat Intel, Malware & RE, Offensive SecurityΒ· Added 3 Sep 2026, published 4 Aug 2026

socket.devwriteupπŸ›‘οΈ Security

Socket: Fake Corepack Site Distributes Infostealer and Proxyware to Developers

Socket's Threat Research team analyzed corepack[.]org, a fake site impersonating the Node.js Corepack tool that exploits its 2025 removal from Node.js bundling to rank in search results and trick developers into downloading a fake VPN installer. The installer drops OpenShield (an infostealer with browser-data/SSH-key theft, PowerShell execution, and run-key persistence) plus a bandwidth-sharing proxyware component that turns victim machines into proxy exit nodes, while a second click path delivers adware/trojan activity via OperaGXSetup.exe. The post includes full IOCs and details community/OpenJS Foundation takedown efforts against the domain.

CorepackNode.jsnpm+3
OpenShieldApprunnercorepack[.]org+3

Threat Intel, Supply ChainΒ· Published and added 25 Jul 2026

aikido.devwriteupπŸ›‘οΈ Security

SleeperGem: RubyGems supply chain attack targets dormant maintainer accounts

Aikido researchers dissect SleeperGem, a RubyGems supply chain attack where a newly published gem, git_credential_manager, downloaded malicious binaries hosted on a fake git-ecosystem account at git.disroot.org and executed them via shell or PowerShell. The attacker evolved the payload across four versions in nine hours, silencing output, wiring execution into the gems require and load path, and adding a check to skip roughly 30 CI environment variables so it only fires on developer laptops, then used two separate long-dormant maintainer accounts to push the gem as a dependency into the trusted gems Dendreo and fastlane-plugin-run_tests_firebase_testlab with over 574000 downloads. The piece argues this is RubyGems first taste of the dormant-maintainer-account-takeover pattern long seen on npm and PyPI.

RubyGemsVirusTotalPowerShell+1
SleeperGemgit_credential_managerDendreo+2

Supply ChainΒ· Added 3 Sep 2026, published 19 Jul 2026

xygeni.iowriteupπŸ›‘οΈ Security

FauxUV campaign (Xygeni)

Xygeni details FauxUV, a cluster of PyPI packages (moon-uv, my-magic-uv-helper) that impersonate the popular Rust-based Python package manager uv but carry almost no real functionality. Instead, on Windows they launch JupyterLab with authentication disabled (empty token, bound to 0.0.0.0, XSRF checks off) and, in later versions, expose it to the internet via a Pinggy SSH reverse tunnel, turning a legitimate data-science tool into an open remote shell that inherits the installing user's credentials. The writeup traces the install-time PowerShell trigger moving from setup.py to a separate CLI tool across versions and provides IOCs and detection guidance.

PyPIPythonPowerShell+3
FauxUVmoon-uvmy-magic-uv-helper+2

Supply Chain, Threat IntelΒ· Published and added 18 Jul 2026

socket.devwriteupπŸ›‘οΈ Security

Socket: Operation Muck and Load

Socket details "Operation Muck and Load," a campaign starting with a malicious Go module (github.com/kaleidora/dnsub-scanning-tool) that impersonates a DNS scanner but launches hidden PowerShell to fetch and decode a multi-layer, XOR-encrypted loader. The loader resolves encrypted payload locations from public dead drops (Pastebin, GitHub, YouTube, Instagram, Telegram, Google Docs), retrieves a password-protected .7z archive masquerading as Microsoft Photos, and deploys AsyncRAT/Quasar/Remcos-style RATs and Vidar infostealer. Pivoting from the module, Socket uncovered 222 GitHub repositories across 190 accounts using automated force-push workflows tied to a single email (ischhfd83@rambler.ru) to fake activity and credibility, some directly hosting Vidar, XMRig/BitMiner, and trojan loaders.

GoGitHubGitHub Actions+3
ischhfd83@rambler.ruAsyncRATQuasar+9

Supply Chain, Threat Intel, Malware & REΒ· Published and added 16 Jul 2026

huntress.comarticleπŸ›‘οΈ Security

Every Ransomware Attack Has a Backstory

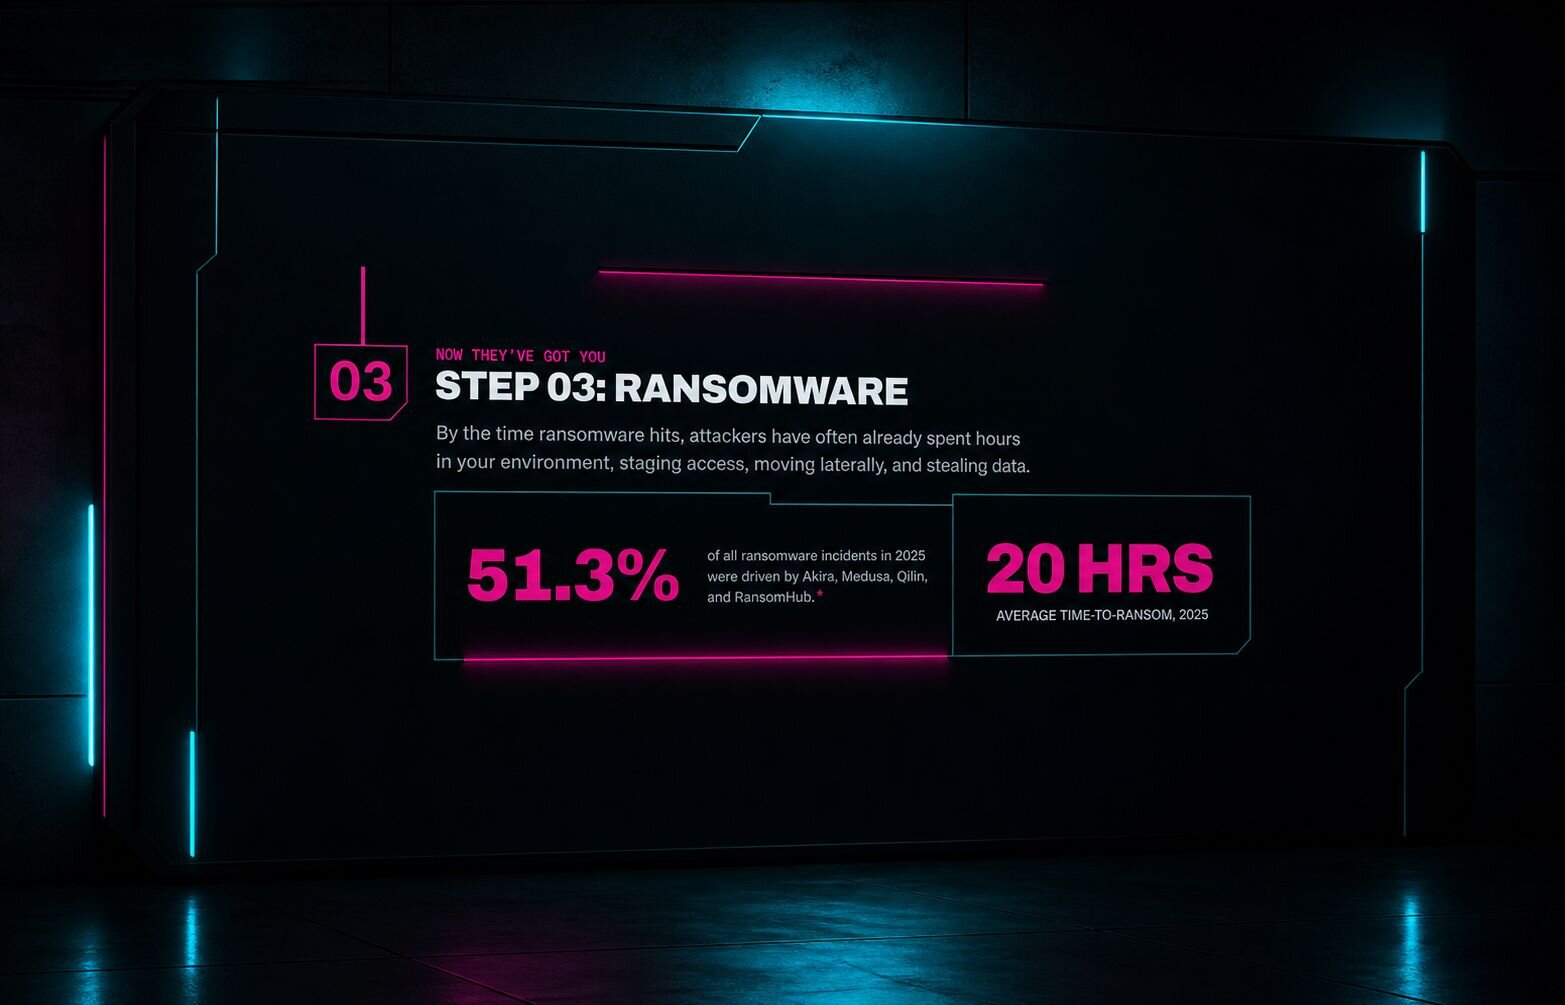
Huntress walks through the ransomware attack chain as a repeatable assembly line: initial access brokers selling footholds (often via infostealers, phishing, or unpatched internet-facing systems), Living-off-the-Land abuse of PowerShell and RMM tools to blend in, and ransomware as the final, visible stage. It cites a real cluster of six ransomware intrusions traced back to the same exposed Citrix NetScaler gateway and session-theft trick culminating in DragonForce ransomware, plus 2026 Cyber Threat Report stats: 37.2% of identity attacks involved suspicious logins, a 277% YoY spike in RMM abuse, ~20 hours average attacker dwell time before detonation, and Akira/Medusa/Qilin/RansomHub driving 51.3% of 2025 ransomware incidents.

Citrix NetScalerPowerShellRDP+1
DragonForceAkiraMedusa+3

Threat Intel, Blue Team & DetectionΒ· Added 3 Sep 2026, published 15 Jul 2026

huntress.comwriteupπŸ›‘οΈ Security

Threat Actors Achieve Persistence After SQL Injection

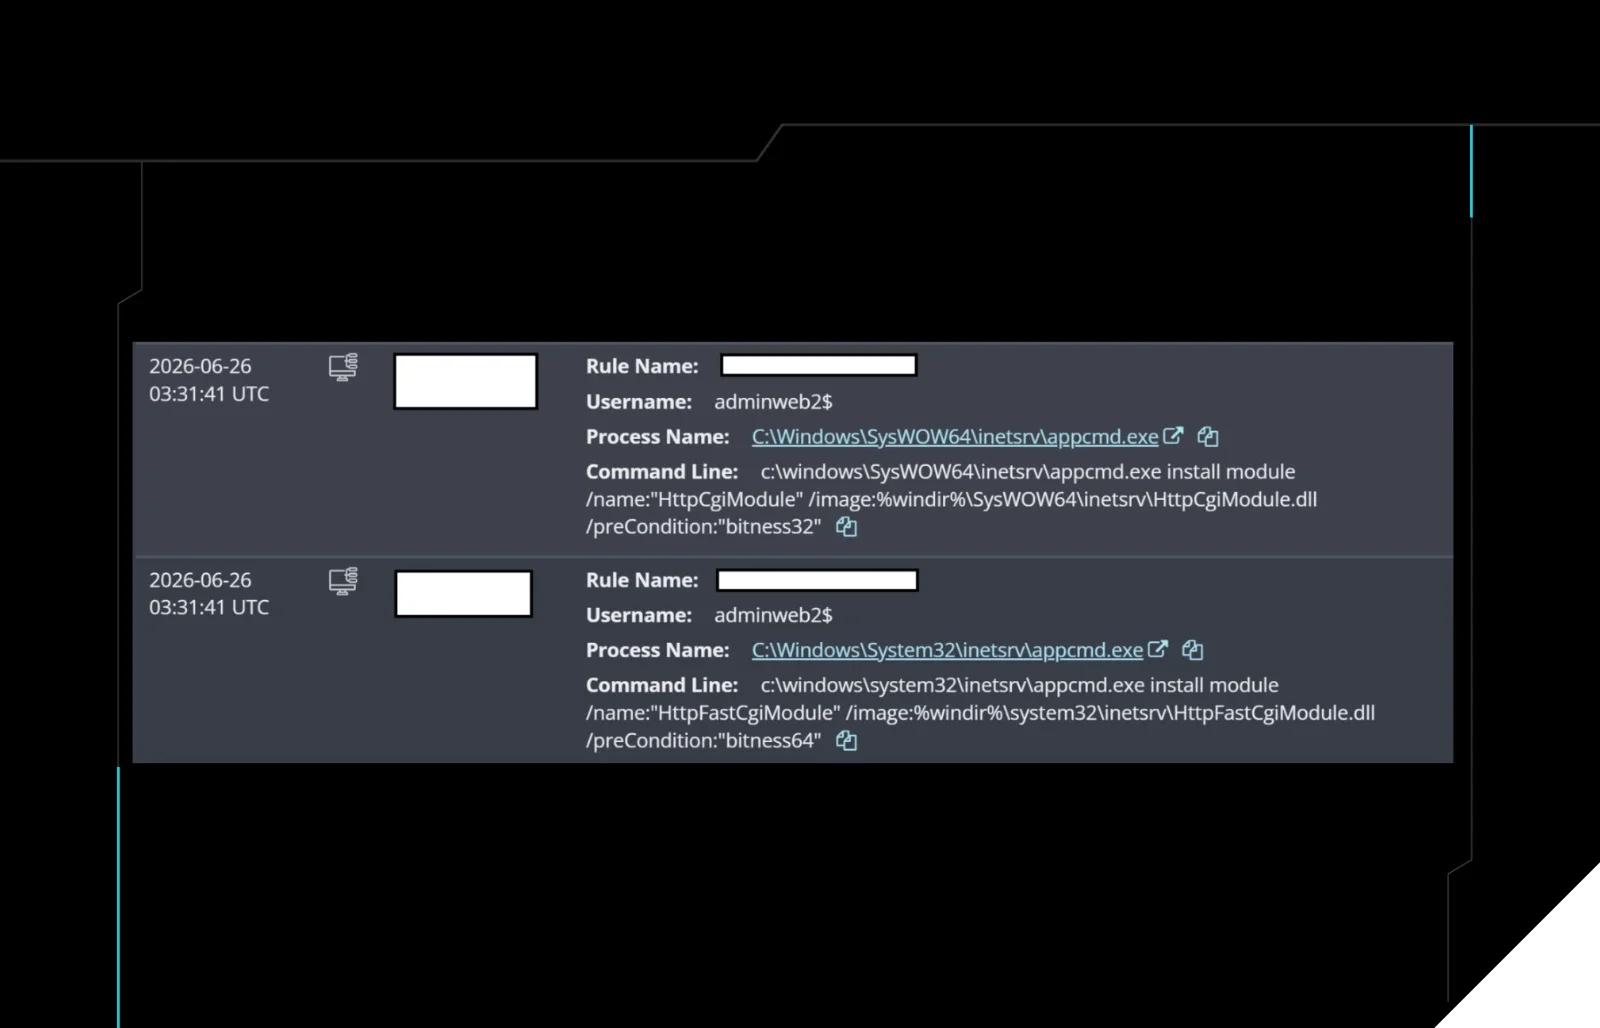
Huntress SOC analysis of a June incident where a threat actor exploited a SQL injection flaw in an IIS/MSSQL web application to gain access, then extensively modified the environment: enabling Terminal Services, creating a rogue admin account (adminweb2$), disabling Windows Defender, deploying BadIIS malicious IIS modules (HttpFastCgiModule.dll, HttpCgiModule.dll) for SEO fraud, installing the XMRig cryptominer with nssm.exe persistence and hidden/system file attributes, and dropping additional PowerShell/batch payloads (qdcjoke1.2.ps1, c_joke1.2.ps1) via base64-encoded PowerShell and Out-of-Band Application Security Testing (OAST) exfiltration channels (oastify.com).

Microsoft SQL ServerIISPowerShell+2
BadIISXMRignssm.exe+6

Threat Intel, Blue Team & Detection, AppSecΒ· Added 3 Sep 2026, published 13 Jul 2026

huntress.comwriteupπŸ›‘οΈ Security

AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

Huntress recovered and reconstructed "Untitled1.ps1," a PowerShell Active Directory enumeration script used by an attacker during a June 3 incident via RDP access with compromised credentials, and identified it as AI-generated ("vibe-coded") based on artifacts like an unedited LLM placeholder hostname, a "FULLY FIXED" prompt-iteration title, over-engineered five-method DC-discovery fallback logic, and gratuitous colored console/HTML reporting output. The attack chain paired this bespoke recon tool with off-the-shelf abuse of s5cmd (legitimate AWS S3 CLI used for exfiltration) and SharpShares (share enumeration), illustrating how LLM-generated one-off malware evades hash/signature-based detection and pushes defenders toward behavioral analytics on Active Directory enumeration patterns.

PowerShellActive DirectoryRDP+2
SharpShares

Threat Intel, Blue Team & Detection, Offensive SecurityΒ· Added 3 Sep 2026, published 8 Jul 2026

huntress.comarticleπŸ›‘οΈ Security

LoTL Abuse: How to Spot It vs. Normal Admin Activity | Huntress

Huntress SOC breaks down how to differentiate legitimate admin use of native tools (PowerShell, WMI, RMM software) from living-off-the-land (LoTL) abuse by attackers, offering a four-point pressure test: who used the tool, where it ran, how it launched, and what followed. It includes real detection examples such as attackers using the legitimate RMM tool Action1 to deploy ScreenConnect for persistent access, a malicious process chain spawning from bomgar-scc.exe, and an LLM-generated script with code comments revealing Telegram-based exfiltration.

PowerShellWMIScreenConnect+2
bomgar-scc.exe

Blue Team & Detection, Threat IntelΒ· Added 3 Sep 2026, published 8 Jul 2026

dfir.chwriteupπŸ›‘οΈ Security

Fantastic clear-text passwords and where to collect them (Part 2 - Windows)

A DFIR.ch deep-dive on stealthier alternatives to LSASS dumping for harvesting Windows cleartext credentials, covering WDigest re-enablement, PowerShell ConsoleHost_history.txt, AD user-attribute leaks, Group Policy Preferences (GPP) cPassword, and rogue Security Support Provider (SSP), Password Filter DLL, and Network Provider DLL registration. Each technique is illustrated with real incident-response case data (registry commands, malicious DLL names like kerberos_sp.dll and mimilib.dll, and exfiltrated log paths), paired with Sysmon Event ID 13/11 detection guidance and hardening recommendations (disabling custom SSPs, Protected Event Logging).

WindowsPowerShellActive Directory+3
CVE-2023-36036ProjectSauronRaccoon Stealer+3

Offensive Security, Blue Team & DetectionΒ· Added 3 Sep 2026, published 28 Jun 2026

huntress.comwriteupπŸ›‘οΈ Security

From Code to Coverage (Part 6): What netlogon.log Sees That Event 1644 Never Will

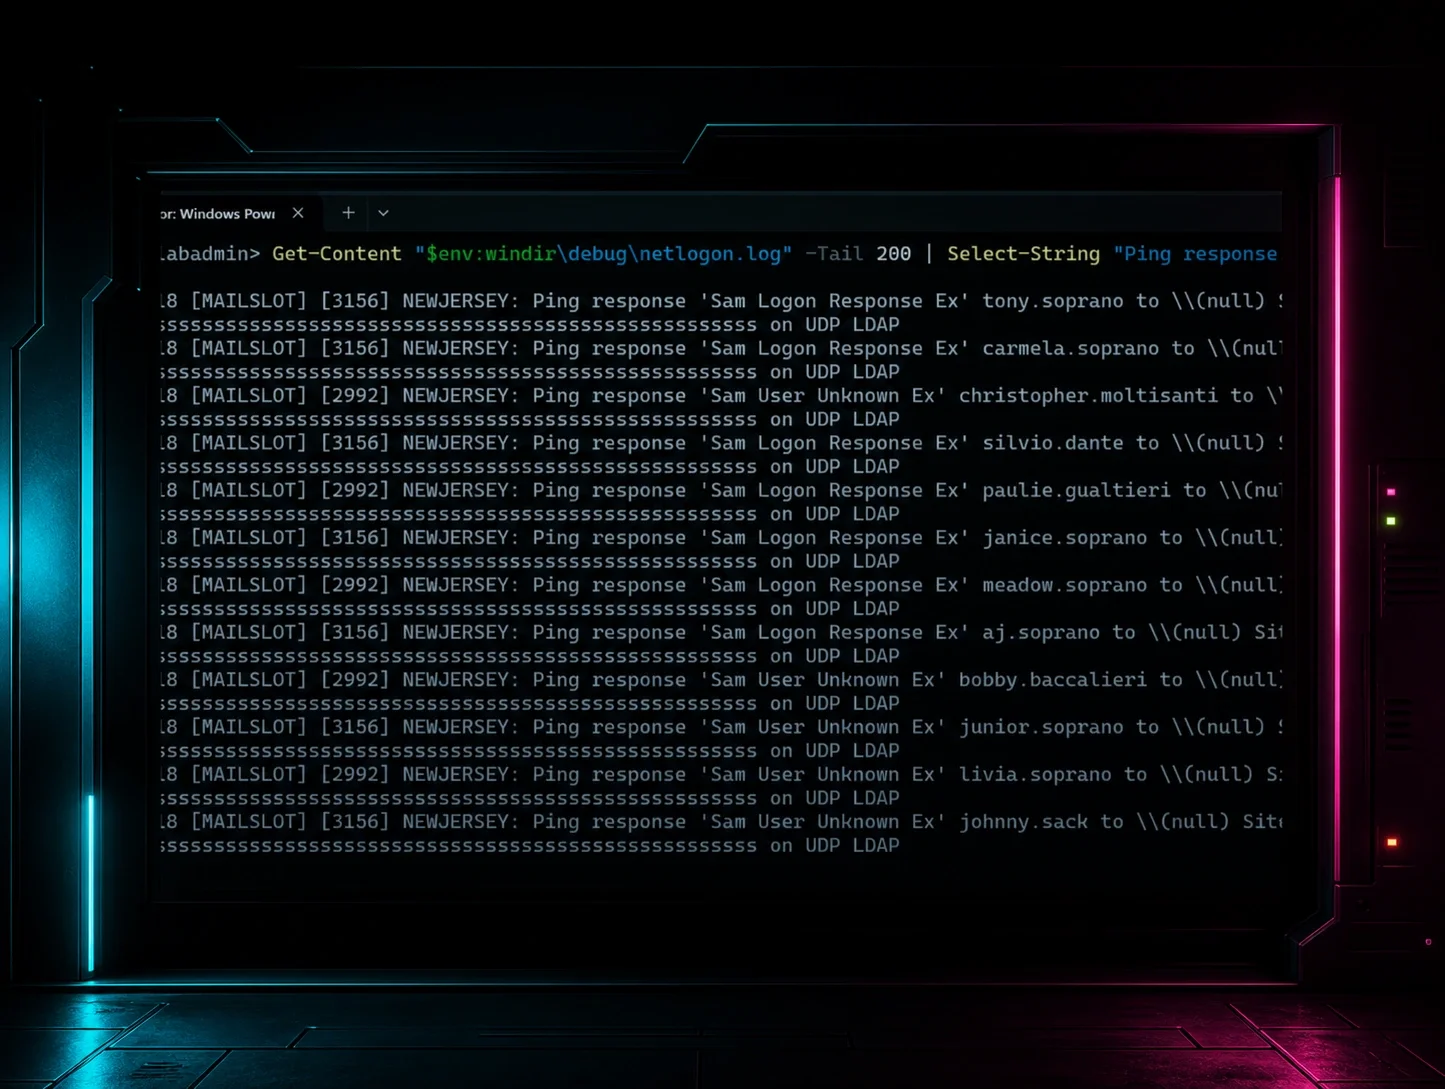
Part 6 of Huntress's "From Code to Coverage" series reverse-engineers ldapnomnom's LDAP Ping (cLDAP-style) Active Directory username enumeration technique, tracing its Go source down to the Windows Filtering Platform to test the tool's claim of generating "no Windows audit logs." Lab testing shows Event 1644 never fires for LDAP Ping (it's processed by netlogon.dll, not the ntdsa.dll LDAP engine it monitors), but netlogon.log captures every queried username including disabled-account detail attackers can't see, while Event 5156 attributes source IP for ldapnomnom's TCP connections β€” a gap that disappears entirely if an attacker switches to true UDP cLDAP (as demonstrated with a custom cldap_ping.py), leaving only MDI's threshold-based external ID 2437 as network-layer coverage. The piece also audits the ldeep tool's enum_users transport and provides a PowerShell correlation script joining netlogon.log and Event 5156 within a 5-second window.

Active DirectoryLDAPWindows+3
ldapnomnomEvent 1644Event 5156+12

Blue Team & Detection, Offensive Security, Identity & AccessΒ· Added 3 Sep 2026, published 24 Jun 2026

snyk.iowriteupπŸ›‘οΈ Security

A Forgotten Contributor Account Compromised the Entire Mastra npm Package Scope

Snyk details how a dormant, never-revoked npm contributor account (ehindero) was used to republish the entire @mastra scope (142+ packages, ~4M monthly downloads for @mastra/core alone) with an injected dependency, easy-day-js, a byte-for-byte dayjs impersonator. The postinstall hook in easy-day-js@1.11.22 disables TLS verification, pulls a second-stage payload from a raw IP, and drops a cross-platform cryptocurrency wallet stealer plus a RAT with OS-specific persistence (LaunchAgent, systemd unit, PowerShell staging) that beacons every 10 minutes over a self-signed wolfSSL certificate. The piece covers detection steps, the Snyk advisory (SNYK-JS-EASYDAYJS-17353313), and draws parallels to the earlier Axios npm compromise attributed by Microsoft to Sapphire Sleet (BlueNoroff).

npmNode.jsSnyk+2
Mastraeasy-day-jsSNYK-JS-EASYDAYJS-17353313+4

Supply Chain, Malware & RE, Blue Team & DetectionΒ· Added 3 Sep 2026, published 16 Jun 2026

huntress.comwriteupπŸ›‘οΈ Security

Potemkin Loader & RMMProject The Anatomy of a ClickFix Attack

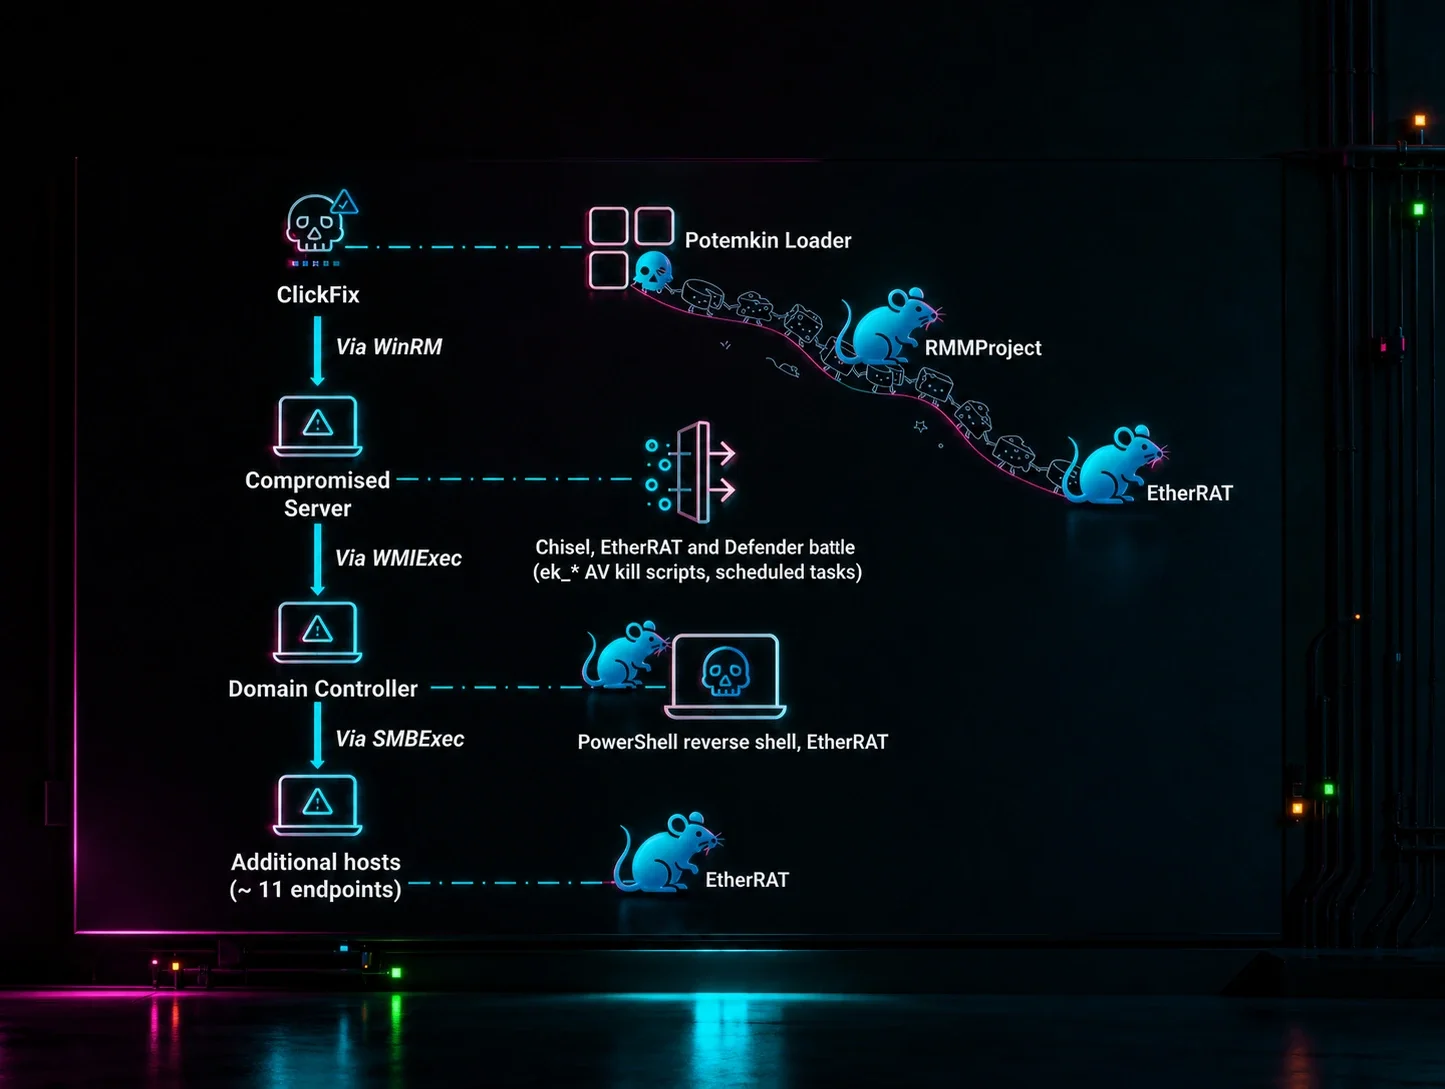
Huntress tears down a May 2026 ClickFix intrusion that escalated from a single unmonitored endpoint to hands-on-keyboard compromise of 11 hosts. The chain starts with a pcalua.exe/mshta.exe LOLBIN abuse to run a remote HTA that silently installs an MSI, dropping Potemkin, a custom x64 DGA-based loader (XorShift32 seed 151678, custom byte cipher, reflective in-memory DLL loading), which fetches RMMProject, a 4.4MB LuaJIT-scriptable module with 15 task types including Chrome App-Bound Encryption bypass via DLL injection into Chrome's IElevator COM interface, Firefox NSS credential theft, and a hidden-desktop remote-control (RTSC) module. The attackers also deployed EtherRAT (an EtherHiding Node.js backdoor resolving C2 from an Ethereum smart contract) and a renamed Cloudflare tunnel client, then moved laterally via WMIExec/SMBExec/WinRM with an AMSI-bypass PowerShell loader to reach the domain controller.

WindowsWindows DefenderChrome+3
ClickFixEtherHidingPotemkin loader+8

Malware & RE, Threat Intel, Offensive SecurityΒ· Added 3 Sep 2026, published 16 Jun 2026

huntress.comwriteupπŸ›‘οΈ Security

Inside .NET Loader Analysis: From Malspam to In-Memory Loader

Huntress SOC dissects a multi-stage infection chain that begins with a malspam HTML attachment routed through a legitimate Google DoubleClick tracking link to evade reputation filters, before landing on a self-personalizing phishing kit and dropping a ZIP with a heavily obfuscated JScript loader. The chain cascades through PowerShell droppers into a .NET stager that performs extensive anti-analysis/anti-sandbox checks, disables Windows Defender, patches AMSI (via NtManageHotPatch on Windows 11 24H2) and ETW at the native API level, and uses RunPE process hollowing into InstallUtil.exe or MSBuild.exe to run a final loader that communicates over AES/RSA-encrypted, protobuf-serialized TCP C2 with certificate pinning. The writeup includes GPU-fingerprinting behavior, persistence via registry Run keys and randomized scheduled tasks, and concrete detection/hardening recommendations.

.NETPowerShellWindows Defender+2
InstallUtil.exeMSBuild.exeNtManageHotPatch

Malware & RE, Threat Intel, Blue Team & DetectionΒ· Added 3 Sep 2026, published 3 Jun 2026

huntress.comwriteupπŸ›‘οΈ Security

The Gentleman Ransomware | Defense Evasion TTPs Uncovered | Huntress

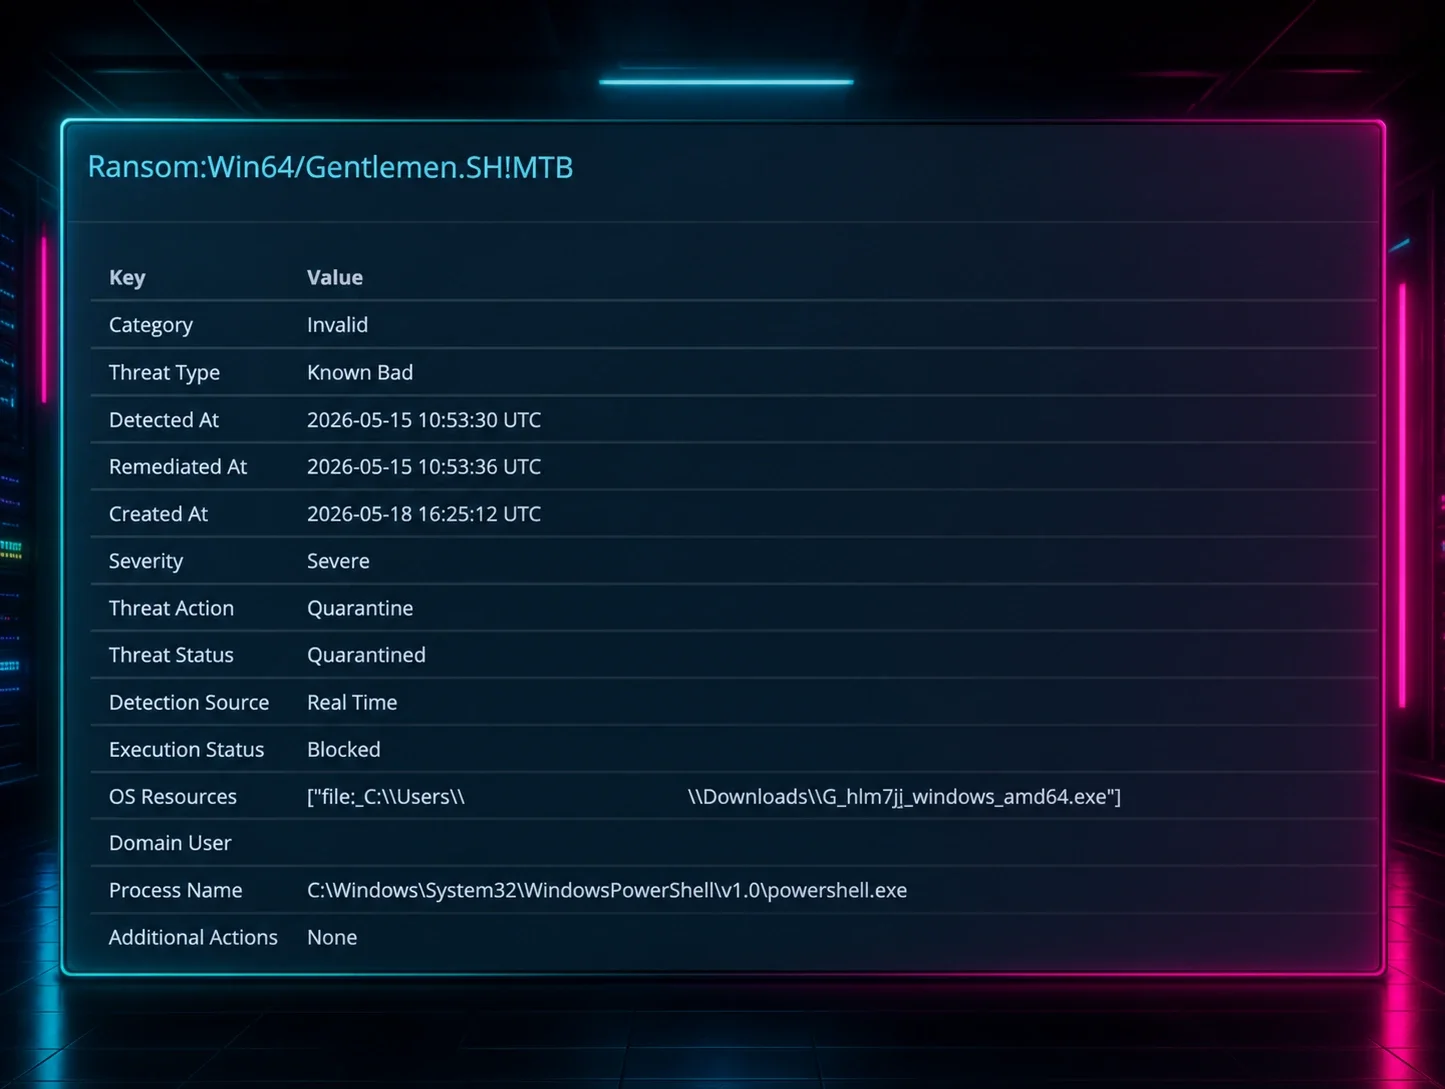
Huntress SOC details two Gentlemen ransomware incidents showing Windows Event Log clearing, PowerShell-based Defender tampering, and Scheduled Task persistence via a fake svchost32.exe creating a SOCKS proxy C2 connection. Ties findings to a leaked internal RaaS database revealing CVE-2024-55591 exploitation and infrastructure links to Qilin and Lazarus Group.

HuntressPowerShellWindows Defender+3
CVE-2024-55591The GentlemenQilin+5

Threat Intel, Blue Team & DetectionΒ· Added 3 Sep 2026, published 21 May 2026

huntress.comwriteupπŸ›‘οΈ Security

The 60ms Window: How Event 5156 Solves the ADWS Attribution Problem

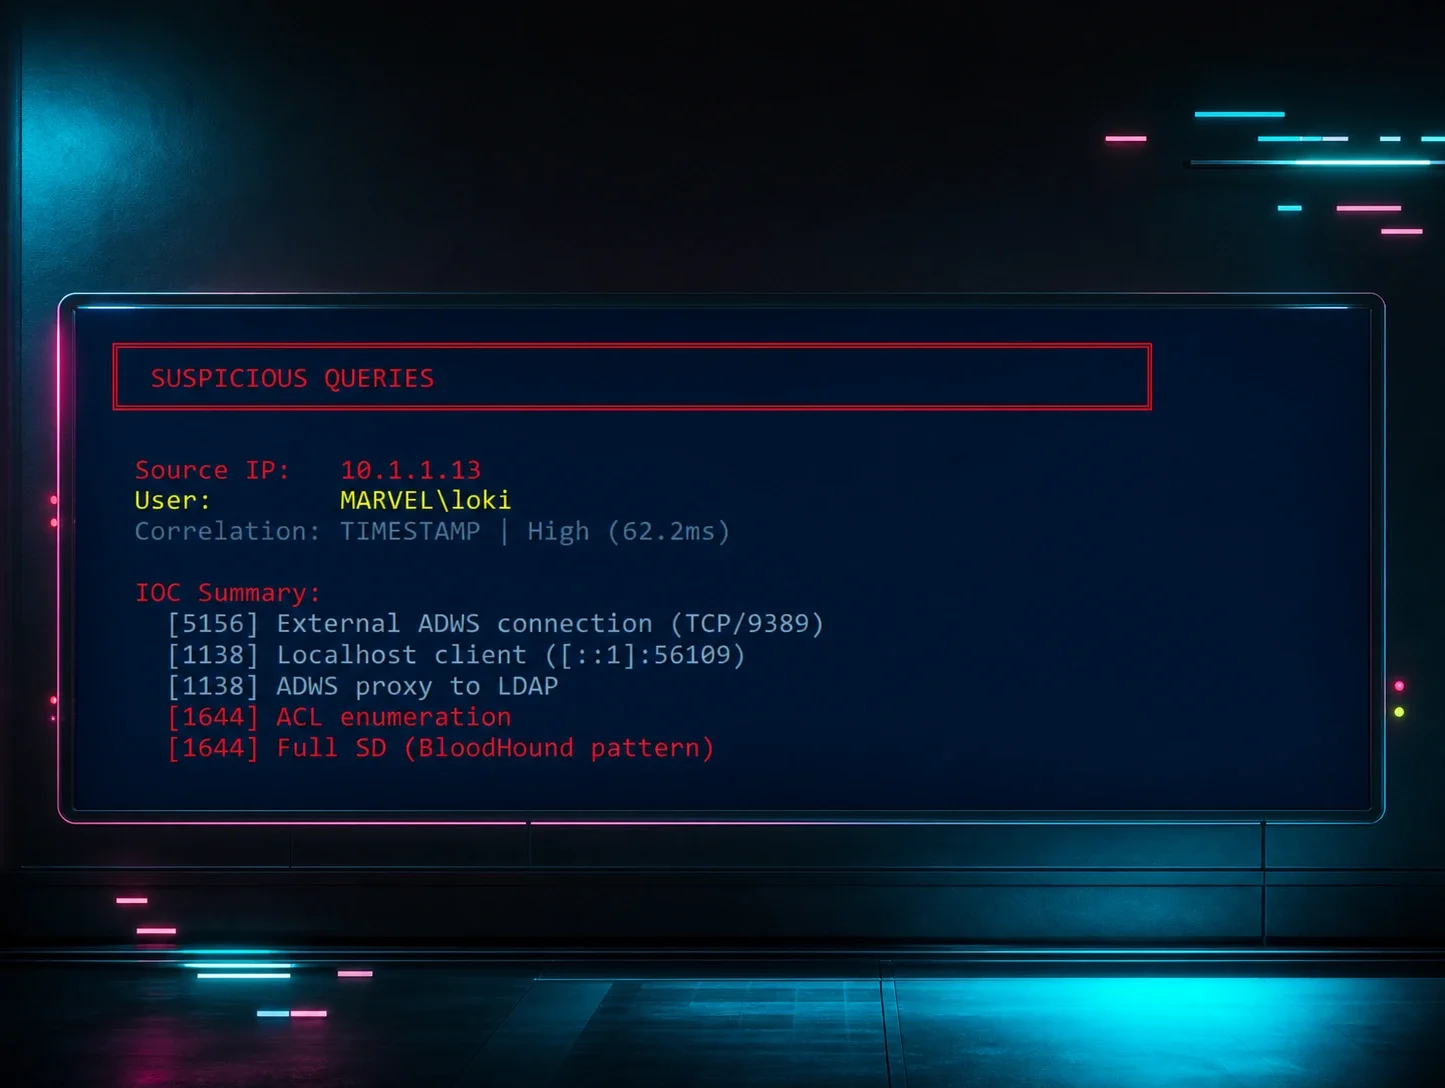
Huntress researchers solve the long-standing 'ADWS attribution problem' where tools like SOAPy abuse Active Directory Web Services to hide the attacker's real source IP behind localhost ([::1]) in LDAP diagnostic logging (Event 1644). By correlating Windows Filtering Platform Event 5156 (which captures the real inbound source IP on port 9389 before ADWS proxies to loopback) with Event 1138 (ADWS session) and Event 1644 (LDAP query) using a stable ~60-80ms timestamp window, they demonstrate reliable attribution even when port-based correlation fails due to log rollover. The post includes a released PowerShell script (Get-ADWSAttribution.ps1) and addresses the false-positive concern of RSAT tools also using ADWS via pattern detection on suspicious 1644 query attributes.

Active DirectoryBloodHoundPowerShell+3
Event 1644Event 5156Event 1138+4

Blue Team & Detection, Offensive SecurityΒ· Added 3 Sep 2026, published 9 Apr 2026

huntress.comwriteupπŸ›‘οΈ Security

The ADWS Architecture That Hides PowerShell AD Enumeration

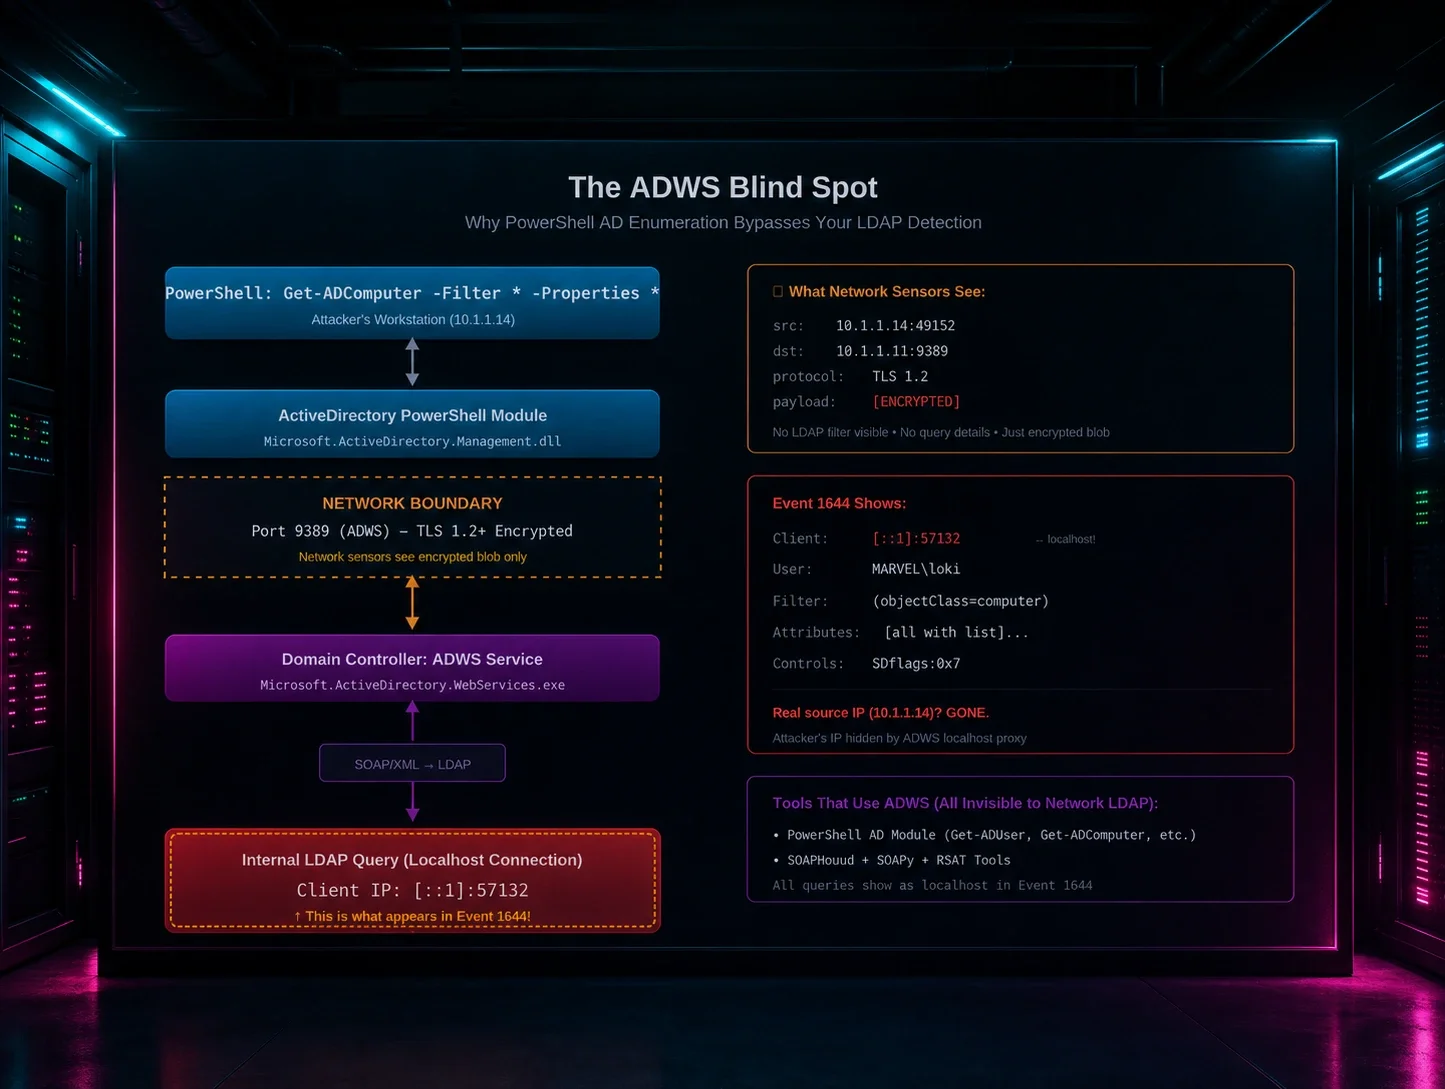
Part 5A of Huntress's LDAP/AD detection series explains why native PowerShell commands like Get-ADComputer -Properties * evade traditional LDAP-based detections: PowerShell's ActiveDirectory module uses Active Directory Web Services (ADWS) over encrypted SOAP on port 9389 rather than LDAP on 389/636, and the resulting Event 1644 log shows the query originating from localhost ([::1]) instead of the attacker's real IP. The author shows how to correlate Event 1644 with ADWS connection/session events (1138, 1139, 1166, 1167) via shared Operation ID to reconstruct full enumeration sessions, and flags the "[all_with_list]" attribute prefix and "SDflags:0x7" server control as high-fidelity indicators of PowerShell bulk property/security-descriptor dumps (as used by tools like BloodHound). It also demonstrates that case obfuscation of cmdlets (e.g., geT-aDcompUTER) is irrelevant at the LDAP layer since PowerShell is case-insensitive and translates to standard LDAP filters before reaching the DC.

PowerShellActive DirectoryLDAP+2
Event 1644Event 1138Event 1139+2

Blue Team & Detection, Offensive SecurityΒ· Added 3 Sep 2026, published 8 Apr 2026

huntress.comarticleπŸ›‘οΈ Security

That β€œFriendly” Prompt is ClickFix

Huntress overview of ClickFix, a social-engineering technique that tricks users into pasting and executing attacker-supplied commands into PowerShell, Run dialogs, or terminals (via fake CAPTCHA/human-verification or tech-support lures) rather than delivering malware through links or attachments. The post cites Huntress 2026 Cyber Threat Report data showing ClickFix accounts for over 50% of malware loader activity and walks through variant types and a real intrusion chain leading to LummaC2 infostealer compromise.

PowerShellHuntressWindows+2
ClickFixLummaC2

Threat IntelΒ· Added 3 Sep 2026, published 25 Mar 2026

huntress.comwriteupπŸ›‘οΈ Security

Data Exfiltration and Threat Actor Infrastructure Exposed

Huntress SOC details two related incidents where threat actors used PsExec for privilege escalation, a scheduled task ("Recovery Diagnostics") to run base64-encoded PowerShell that configured a renamed copy of restic (winupdate.exe) pointed at a Wasabi S3 bucket, then disabled/removed VIPRE Business Agent and Windows Defender before deploying INC ransomware. A second, near-identical prior incident on 9 February reused the same AWS access keys and used HRSword to disable Acronis security tooling, and the same TTPs were independently documented by the Cyber Centaurs team on 22 January 2026. The post highlights detection gaps (incomplete agent deployment, no SIEM) and notes RestartManager API telemetry (also seen with Akira) as a ransomware-encryption indicator.

PowerShellWindowsWindows Defender+3
INC ransomwareAkiraHRSword+2

Blue Team & Detection, Threat IntelΒ· Added 3 Sep 2026, published 12 Mar 2026

huntress.comwriteupπŸ›‘οΈ Security

Dissecting CrashFix: KongTuke's New Toy

Huntress dissects a KongTuke campaign built around NexShield, a malicious Chrome extension impersonating uBlock Origin Lite that induces a deliberate browser DoS/crash and then displays a fake "CrashFix" repair prompt to trick users into pasting a malicious PowerShell command via the Windows Run dialog. The command abuses finger.exe as a LOLBin to fetch and execute layered, obfuscated PowerShell that profiles the victim (domain-joined vs standalone, AV, VM checks), uses weekly-rotating DGA domains, an AMSI patch bypass, and a two-layer AES+XOR encrypted .NET loader ("GateKeeper") with anti-sandbox fingerprinting, ultimately dropping ModeloRAT β€” a newly documented, RC4-encrypted Python RAT reserved for domain-joined corporate hosts β€” while non-domain targets currently only receive a "TEST PAYLOAD" response. The post includes full IOCs and YARA rules for GateKeeper, MintsLoader, and ModeloRAT.

PowerShellChrome.NET+3
KongTukeCrashFixNexShield+7

Threat Intel, Malware & RE, Blue Team & DetectionΒ· Added 3 Sep 2026, published 16 Jan 2026

huntress.comwriteupπŸ›‘οΈ Security

Reflecting on AI in 2025: Faster Attacks, Same Old Tradecraft

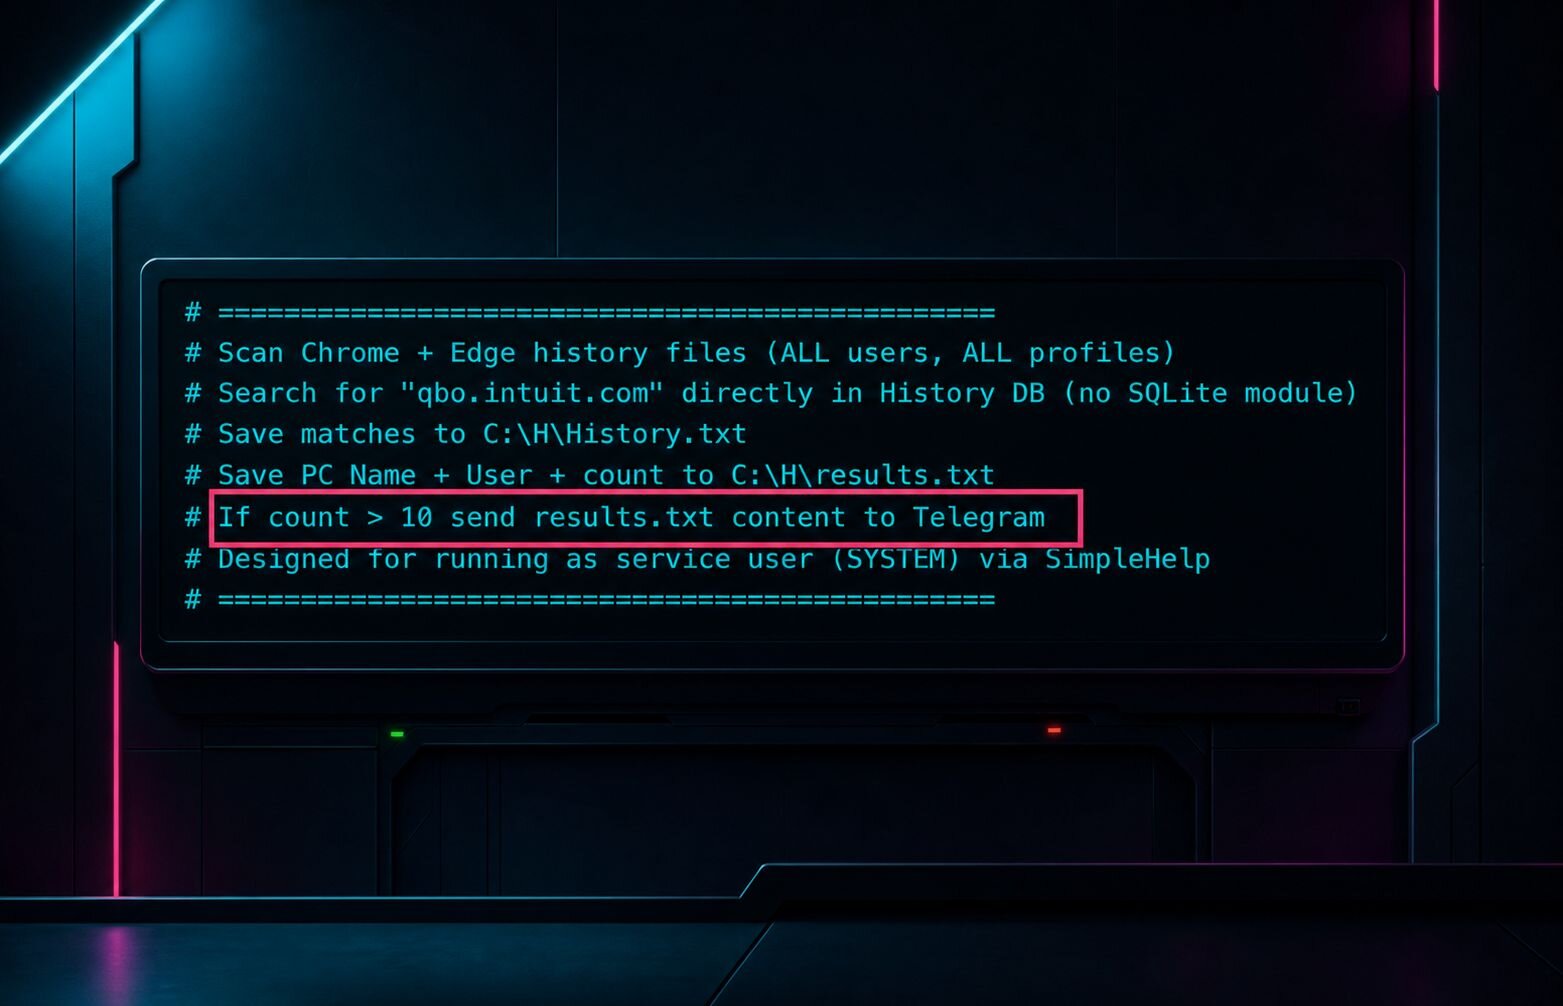
Huntress reviews four 2025 intrusions where adversaries used LLMs (ChatGPT, DeepSeek, Gemini) to draft PowerShell tradecraft: an RDP-brute-forced credential dumper, a Veeam credential-theft script (v.ps1) over WinRM, an iterated Chrome/Edge history-scraping script chain (qb_check.ps1 β†’ coinbase_check.ps1 β†’ secure.chase.ps1) exfiltrating to Telegram, and a fully-featured Chrome extension RAT ("Telegram Agent + Cookies") beaconing to a C2 for cookie/screenshot/history exfiltration. The pattern across cases: AI speeds up authoring (odd comments, Cyrillic strings, verbose AI-style formatting) but doesn't produce novel primitives, so existing detections (EDR, telemetry, MFA, segmentation) still catch it.

HuntressPowerShellScreenConnect+5
Telegram Agent + Cookiesqb_check.ps1coinbase_check.ps1+2

Threat Intel, Blue Team & Detection, AI SecurityΒ· Added 3 Sep 2026, published 12 Jan 2026

huntress.comwriteupπŸ›‘οΈ Security

#ShadyHacks with Kyle Hanslovan

Huntress CEO Kyle Hanslovan demonstrates a full modern account-takeover chain against Microsoft 365: buying stolen credentials on a dark web marketplace, using a ChatGPT-crafted phishing email with a fake SharePoint link to trigger a ClickFix-style CAPTCHA that tricks the victim into pasting a PowerShell command, stealing active session cookies with an infostealer, and importing them via the Cookie Editor browser extension to bypass MFA entirely. It then covers post-compromise tradecraft β€” malicious inbox rules to forward/hide sensitive emails, Teams-based social engineering of IT support to register new MFA devices, and abusing email-based password resets on non-SSO apps (payroll, CRM) β€” plus defensive recommendations (conditional access, inbox rule auditing, DMARC/DKIM/BIMI, session revocation processes, security awareness training).

Microsoft 365PowerShellChatGPT+1
ClickFixsession hijackingtoken impersonation+1

Identity & Access, Offensive Security, Threat IntelΒ· Added 3 Sep 2026, published 26 Nov 2025

huntress.comwriteupπŸ›‘οΈ Security

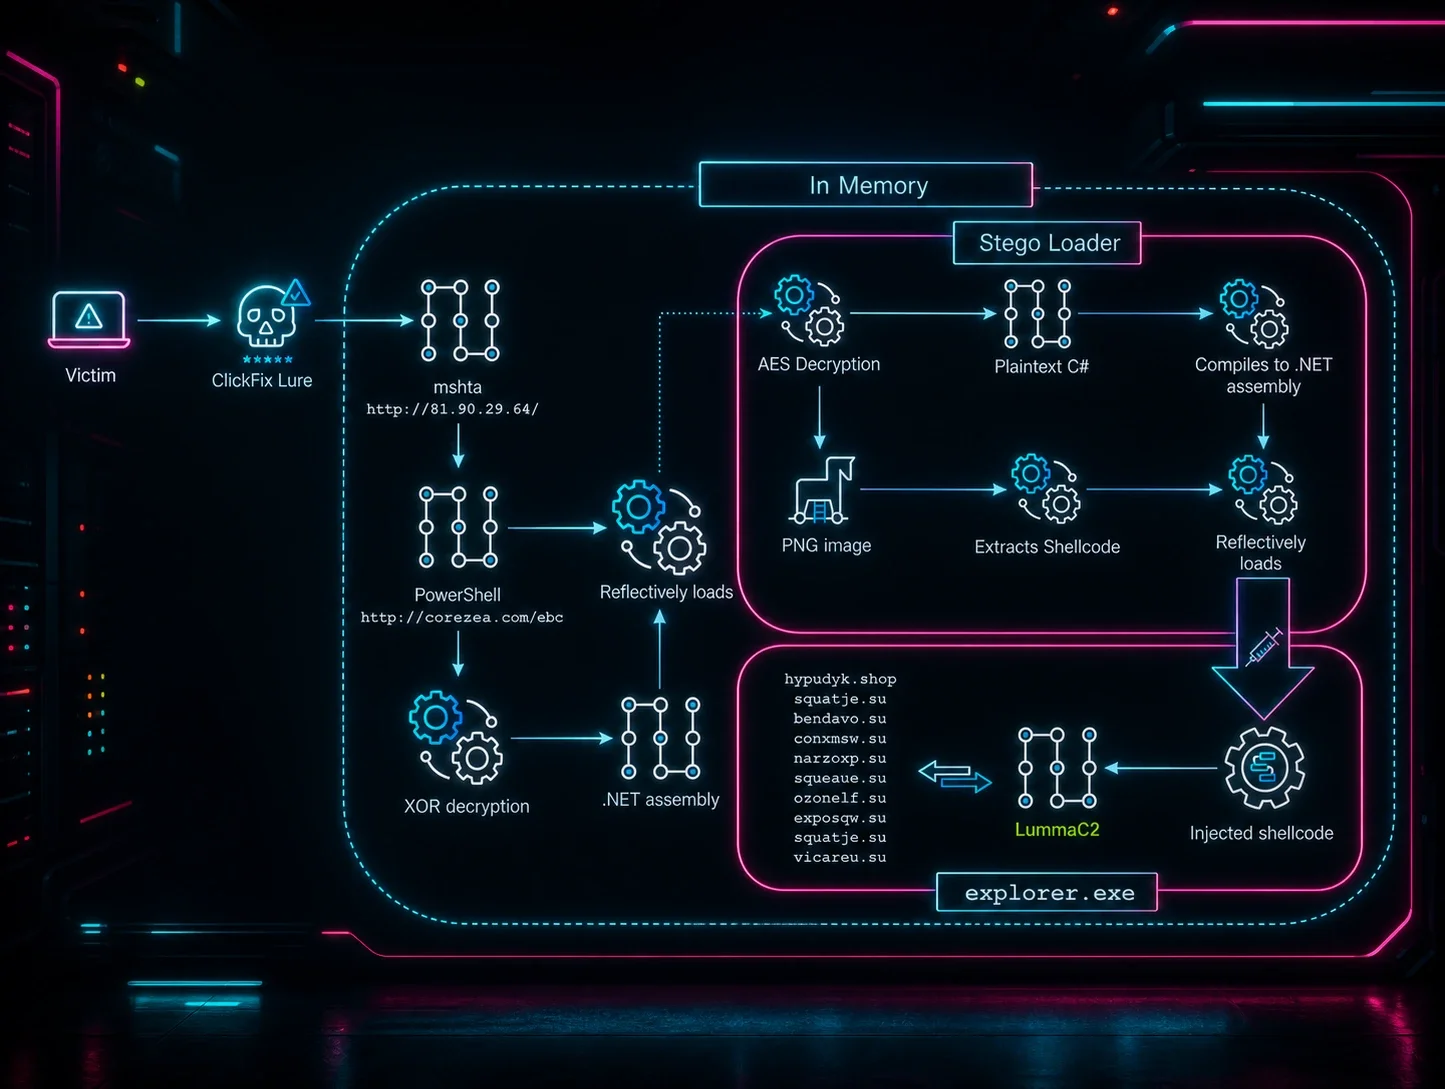
ClickFix Gets Creative: Malware Buried in Images

Huntress documents a multi-stage ClickFix campaign (fake "Human Verification" and fake Windows Update lures) that copies an mshta command to the clipboard, which chains through obfuscated PowerShell and reflectively-loaded .NET assemblies to a custom steganographic loader. The loader extracts Donut-packed shellcode encoded in the pixel data of an AES-encrypted PNG (via a red-channel XOR scheme) and injects it into explorer.exe, ultimately deploying LummaC2 or Rhadamanthys infostealers; the writeup includes deobfuscation walkthroughs (dnSpy), a Python re-implementation of the stego algorithm, IOCs, and mitigation guidance (disabling the Run box, RunMRU auditing).

.NETPowerShellWindows+2
ClickFixLummaC2Rhadamanthys+2

Malware & RE, Threat Intel, Blue Team & DetectionΒ· Added 3 Sep 2026, published 24 Nov 2025

huntress.comarticleπŸ›‘οΈ Security

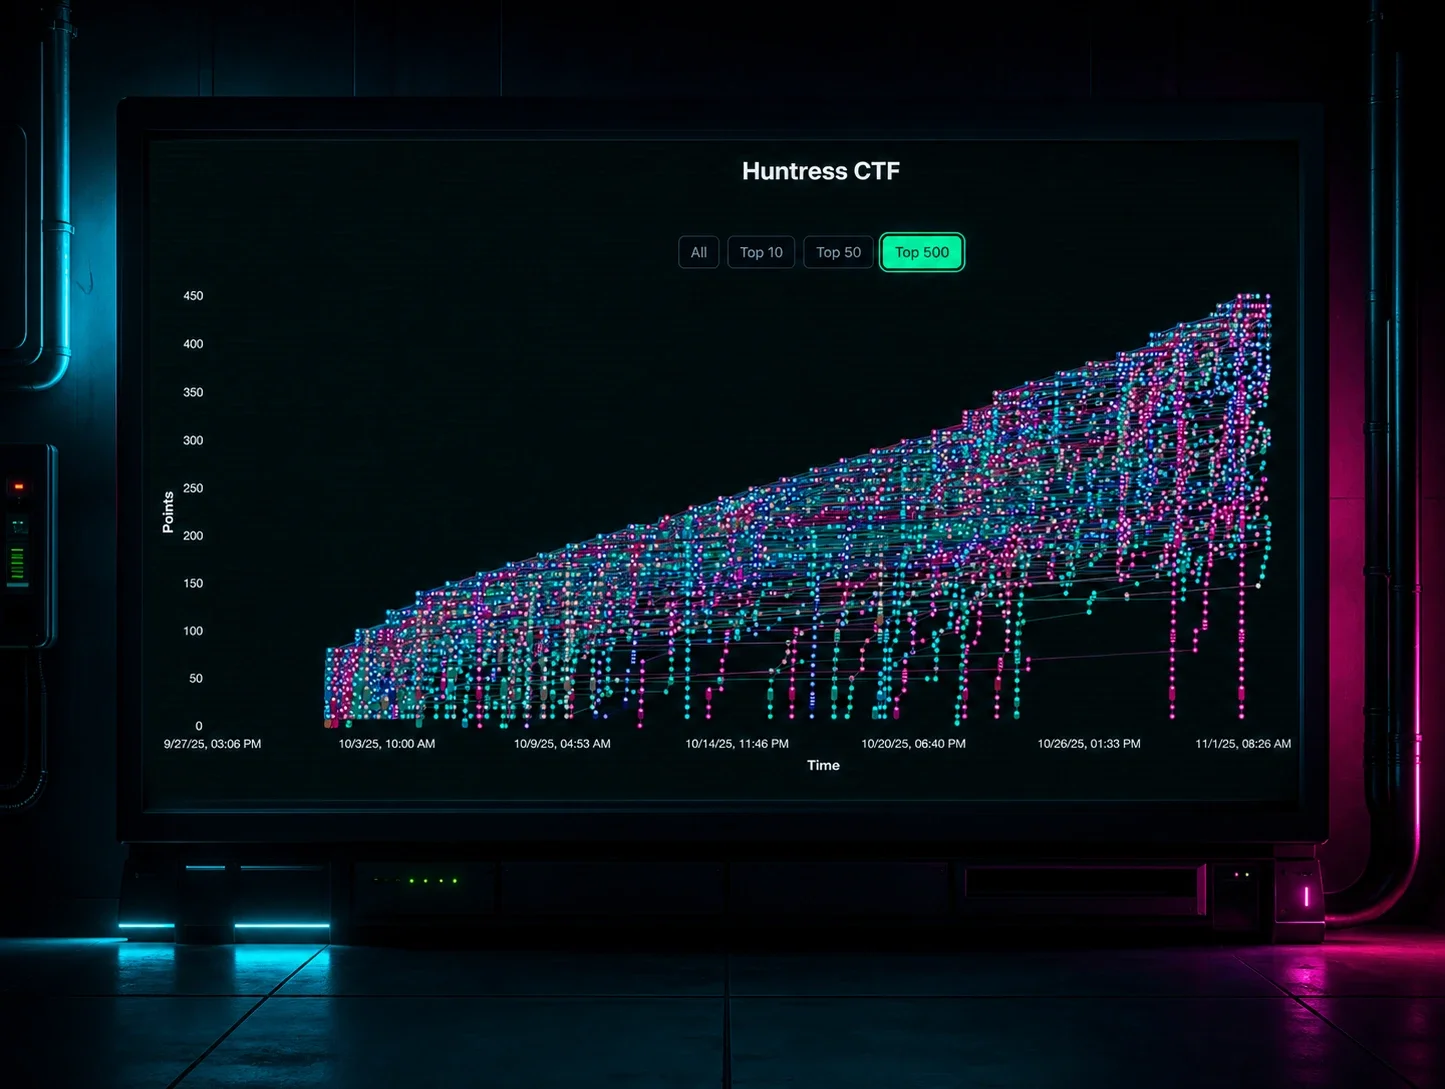
Deobfuscating Files for Flags: Huntress CTF 2025 Retro

Huntress's recap of its October 2025 CTF event (11,898 registered users, 6,892 teams), covering challenge highlights like an AutoIT-decompiled cryptocurrency stealer ('Sandy'), a Rust-reimplemented supply-chain malware challenge ('Rust Tickler'), a Lua infostealer ('My Hawaii Vacation'), a Linux kernel rootkit reverse-engineering challenge ('Root Canal'), a nested PowerShell malware challenge ('Lizard'), an EntraID phishing challenge ('Angler'), and OSINT/DFIR challenges, with links to community-authored writeups for several. It also notes operational bloopers, including a database overload from launch traffic and participants triggering real Microsoft Defender alerts by analyzing malware outside isolated VMs.

AutoITPowerShellRust+3
John HammondMatt KielyHuskyHacks

Learning, Malware & REΒ· Added 3 Sep 2026, published 6 Nov 2025

dfir.chwriteupπŸ›‘οΈ Security

Tear Down The Castle - Part 1

DFIR.ch analyzed 250 PingCastle audit reports collected from real incident response and compromise assessment engagements to quantify common Active Directory misconfigurations, mapping each finding to The Ten AD Commandments. It covers ADCS certificate template abuse (ENROLLEE_SUPPLIES_SUBJECT, referencing SpecterOps Certify tool and the Certified Pre-Owned research), Kerberoastable and over-privileged service accounts, weak or non-expiring passwords, missing LAPS and PowerShell script block logging, and unrestricted MachineAccountQuota, each with concrete affected-domain statistics from real-world cases.

Active DirectoryKerberosMimikatz+3
APT29SpecterOPSCertify+2

Offensive Security, Blue Team & DetectionΒ· Added 3 Sep 2026, published 19 Jan 2025

dfir.chwriteupπŸ›‘οΈ Security

Microsoft Defender XDR's Deception Technology

A DFIR investigation into mysterious domain admin accounts (e.g. "amol.paulson") appearing across an organization's devices, traced back to Microsoft Defender XDR's built-in deception capability, which auto-generates decoy accounts and hosts as lures. The post details how to identify a decoy-account login via local (not network) authentication preceded by a specific PowerShell script execution, and decodes the base64 JSON descriptor blob (containing DetectionKeys, LureDeploymentContext, UserRid, etc.) that reveals which decoy account triggered the alert β€” useful so defenders don't mistake this feature for an intrusion.

Microsoft Defender XDRPowerShellActive Directory

Blue Team & DetectionΒ· Added 3 Sep 2026, published 10 Oct 2024

dfir.chwriteupπŸ›‘οΈ Security

ScriptBlock Smuggling

A DFIR.ch lab writeup that tests BC-Security's ScriptBlock Smuggling technique, which abuses PowerShell's ScriptBlockAst to make malicious code execute while a spoofed benign-looking script gets written to the Script Block log (Event 4104), bypassing AMSI without reflection or memory patching. The author shows that while the 4104 log is indeed spoofed, PowerShell Module Logging (Event 4103) still captures the real executed code, and Windows Defender/AMSI flagged the test payload as Trojan:PowerShell/ScriptSmug.A, meaning defenders retain multiple detection opportunities. It also references an AtomicRedTeam test for the technique and notes in-the-wild adoption to deliver Vidar-Stealer.

PowerShellWindows DefenderSplunk
BC-SecurityVidar-StealerAtomicRedTeam+1

Blue Team & Detection, Offensive SecurityΒ· Added 3 Sep 2026, published 13 Sep 2024

0xv1n.github.iowriteupπŸ›‘οΈ Security

Remote Session Enumeration via Undocumented Windows APIs

A reverse-engineering walkthrough of qwinsta.exe showing it uses the undocumented WinStation API (winsta.dll) β€” WinStationOpenServerW, WinStationEnumerateW, WinStationQueryInformationW β€” rather than the documented Terminal Services (WTS) API used in harmj0y's prior PowerShell approach. The author demonstrates that remote session enumeration via these APIs succeeds against a target host even when Remote Desktop is disabled, and provides C++ code to load winsta.dll, resolve the undocumented function pointers via GetProcAddress, and parse the resulting byte-array structures to extract usernames and session state.

WindowsRDP
harmj0yGrzegorz TworekProcess Hacker+5

Offensive Security, Malware & REΒ· Added 3 Sep 2026, published 14 Jul 2024

dfir.chwriteupπŸ›‘οΈ Security

Today I Learned - Instrument ClamAV to extract AutoIT scripts

DFIR.ch shows how to abuse ClamAV's scanning temp-file behavior (clamscan --leave-temps --tempdir=) to extract embedded AutoIT scripts from a compiled .exe, using SimpleLapsGui.exe (flagged by multiple AV vendors) as the example. The recovered autoit.001 script and PowerShell payload are validated against output from the dedicated Python tool autoit-ripper, giving analysts two independent, Windows-binary-free methods for automating AutoIT script extraction during malware/PUA triage.

ClamAVAutoITPowerShell+1
SimpleLAPS-GUIUniversal AutoIT Extractor and De-obfuscatorautoit-ripper

Malware & REΒ· Added 3 Sep 2026, published 9 Jun 2024

dfir.chwriteupπŸ›‘οΈ Security

Removing Traces of RMM Tools

A DFIR researcher analyzes a PowerShell "cleaner" script discovered in an open directory (flagged by Fox_threatintel) and uploaded to VirusTotal, which threat actors use to erase traces of legitimate RMM tools like Atera and Splashtop after gaining access to a victim machine. The script sets the SystemComponent registry flag to hide the software from Apps & Features, deletes Start Menu/ProgramData installer folders (also targeting AnyDesk), and renames the Splashtop Windows Firewall rule to masquerade as a "Cast to Device" service. The author tests the script on a live machine and shows the anti-forensic tricks are shallow β€” toggling SystemComponent back to 0 restores visibility and other forensic artifacts still reveal the software.

PowerShellWindowsAtera+3
Fox_threatintel91.215.85.18

Blue Team & Detection, Malware & REΒ· Added 3 Sep 2026, published 10 May 2024

dfir.chwriteupπŸ›‘οΈ Security

Today I Learned - Device Discovery

dfir.ch documents an incident response investigation where an NDR sensor flagged a suspicious internal port scan. The analyst used EDR telemetry to identify the responsible PowerShell script (hash-verified, Microsoft-signed) invoking Defender for Endpoint's Device Discovery feature (Scan-UdpTcpPorts, Scan-Vnc, Scan-WinRm, etc.), decoding its base64 ScannerArgs to reveal target IPs, MACs, and the CVEs it probes for (CVE-2021-44228, CVE-2022-22965). The scan turned out to be benign legitimate network discovery from Defender for Endpoint, explaining why it triggered an NDR false positive.

PowerShellMicrosoft Defender XDREDR
CVE-2021-44228CVE-2022-22965

Blue Team & DetectionΒ· Added 3 Sep 2026, published 27 Apr 2024

bencteux.frwriteupπŸ›‘οΈ Security

Windows explorer restrictions bypasses - filesystem access

A pentesting-focused writeup explaining how Windows Explorer restrictions NoDrives, NoViewOnDrive, and NoNetConnectDisconnect are configured via registry keys under HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer, and demonstrating multiple practical bypasses (explicit path typing, autocomplete, Run box, Microsoft Edge, cmd.exe/PowerShell, loopback network drive mapping). The author notes these are purely visual restrictions enforced by explorer.exe and are trivially circumvented by any non-Explorer GUI or CLI program, making them insufficient as a security control in kiosk or restricted-desktop environments.

WindowsMicrosoft EdgePowerShell
NoDrivesNoViewOnDriveNoNetConnectDisconnect

Offensive SecurityΒ· Added 3 Sep 2026, published 8 Apr 2024

dfir.chwriteupπŸ›‘οΈ Security

Two in a row - You mitigated wrong (Kentico CMS RCE)

A DFIR consultant details two investigations (five months apart) into a compromised IIS/Kentico CMS server. Attackers exploited a Kentico Staging SyncServer .NET deserialization RCE (via a public exploit and a Metasploit module using the WindowsIdentity gadget chain) to plant a rewrite-rule redirect to Vietnamese black-hat SEO content, then later returned with a malicious IIS native module (HTTPCacheLog.dll) that hooked BeginRequest to execute commands from HTTP cookies, plus multiple .ashx webshells and PrintNotifyPotato.exe for privilege escalation. The piece walks through using Chainsaw, Sysmon, PowerShell logs, and Velociraptor/YARA hunts to trace the intrusion and lists file-hash IOCs.

IISMetasploitSysmon+5
PrintNotifyPotatoDotNetDeserializationWindowsIdentity gadget chain+3

Blue Team & Detection, AppSecΒ· Added 3 Sep 2026, published 6 Mar 2024

Showing 60 of 68

Show more