 4 real? Tracking exploitation and patching of eMudhra’s weak keys
Cloudflare's follow-up on eMudhra's eight trivially recoverable intermediate CA keys (such as 4, 56 and 66), disclosed 19 October 2026. Pingora logging showed about 22,000 handshakes with the weak keys, including about 160 forged certificates made within hours of disclosure. Probes on 50 million challenge pages show many bots, old browsers and Android WebView still trust the chain.
 blog.cloudflare.comwriteupPublished and added 30 Oct 2026🛡️ Security
 Discovering vendor-specific vulnerabilities in Android | Oversecured Blog
Oversecured describes extending its Android scanner to system APIs and to Samsung's Android build, after comparing Google and Samsung framework JARs and about 400 system services. It explains AIDL service permission checks and new control-flow analyses. Examples include Samsung's unchecked semIsBackupEnabled(), a broadcast that reboots the device, and a LaunchAnyWhere in Settings. Samsung had fixed over 60 reported issues.
 oversecured.comwriteupAdded 29 Oct 2026🛡️ Security
 Disclosure of 7 Android and Google Pixel vulnerabilities
Oversecured discloses seven Android vulnerabilities, two of them Pixel-specific, all reported to Google and fixed except one low-severity WebView case. They are the Camera geolocation leak (CVE-2024-0017), a VPN bypass list change (CVE-2023-21383), a Bluetooth permission check flaw (CVE-2024-34719), the WorkSource parcel mismatch (CVE-2023-20963, exploited in the wild by the Pinduoduo app), Device Admin HTML injection (CVE-2021-0600) and a ContentProvider.openFile() caller-context bypass (CVE-2023-21292). Each has root cause and PoC code.
oversecured.comwriteupAdded 29 Oct 2026🛡️ Security NIK C2: The new AI-enabled command-and-control framework
NIK C2 is a newly observed C2 framework with a Go-based 64-bit Windows implant that embeds an OpenAI Chat Completions client (ai_generate command), falling back to the victim's OPENAI_API_KEY. Talos details its 52+ commands, AES-256-GCM over WebSocket with HTTP fallback, credential, wallet and keystroke theft, screen-lock ransomware, AMSI bypass and anti-debug. It also lists a live C2 at 87.120.196[.]120 and total-sitevv[.]lol.
 blog.talosintelligence.comwriteupPublished and added 29 Oct 2026🛡️ Security
 Searchjacked: Hidden Browser Extensions Hijack Searches for 13 Million Users
Searchjacked is Socket's research on 319 browser extensions (about 13.44M users over a decade) that hijack searches to earn ad revenue. The fetched text attributes 200 extensions to named operators such as Intango, System1, Perion, Mutual Media and Kinner Lake, and 119 to unknown operators like "SecuryBrowse" and "Bing-Search". It lists the Yahoo and Bing monetization IDs used to link them. The narrative and technical mechanics are not in the fetched text.
 socket.devwriteupPublished and added 29 Oct 2026🛡️ Security
 Node2Shell: Reproducing CVE-2026-111497 in the Node.js Brotli decoder
Node2Shell is Datadog Security Labs' analysis of CVE-2026-111497, an out-of-bounds write in the Google Brotli 1.2.0 decoder, fixed in Node.js 22.23.4, 24.22.1 and 26.12.1 on 21 October 2026. It explains the unchecked return value in DecodeBlockTypeAndLength(), the read and write primitives, and why code execution is still engineering effort. It lists inbound and outbound exposure paths, behavioral detections and what WAFs miss.
 securitylabs.datadoghq.comwriteupPublished and added 29 Oct 2026🛡️ Security
 PHP2Shell: From the attacker’s perspective
PHP2Shell is the public exploit for CVE-2026-109618 (corrupted internal state at the memory limit, allowing hijack during cleanup) and CVE-2026-109619 (double free used to leak memory and defeat ASLR). Orca ran the GitHub tool unchanged against an unpatched PHP server and got command execution. It then built its own exploit with AI from the patch, which worked on PHP 8.4.26 and WordPress. Fixed in 8.2.35, 8.3.36, 8.4.27 and 8.5.12.
 orca.securitywriteupPublished and added 26 Oct 2026🛡️ Security
 Brotlipocalypse
 is an OSM Security post (24 October 2026) on CVE-2026-111497, an out-of-bounds write in the google/brotli C decoder (1.0.3 through 1.2.0). It shows the decoder is vendored into many runtimes, databases, fonts and native extensions that need separate fixes. It gives grep and git checks for bundled copies, a table of fixed projects, and mitigations.
 opensourcemalware.comwriteupPublished and added 24 Oct 2026🛡️ Security
 Python Packages Vulnerable to Node2Shell
Analysis of CVE-2026-111497 (Node2Shell), an out-of-bounds write in Google's Brotli C decoder, showing it also affects the PyPI packages Brotli (all releases up to 1.2.0) and brotlicffi (up to 1.2.0.2). The author diffed the 1.2.0 and 1.2.1 sdists and confirmed the behaviour with AddressSanitizer. Fixes are Brotli 1.2.1 and brotlicffi 1.2.1.0, both patched without release notes. No advisory database lists either package yet.
opensourcemalware.comwriteupPublished and added 23 Oct 2026🛡️ Security “Next Exploit Opportunities”: How a Threat Actor Used AI to Help Plan and Execute Multiple Types of Cybercrime Activities
Unit 42 analysis of a threat actor, BUGSTER, who ran the Hermes Agent framework with jailbroken DeepSeek V4 and Cursor to plan and run cybercrime. Activity included a WordPress brute force, a MongoDB exfiltration of over 5,200 student records at an Indian university, VoIP fraud planning, Wi-Fi cracking via Vast.ai GPUs, and crypto whale reconnaissance. The report covers the actor's prompt-level safety override, infrastructure (162.243.3[.]92) and attribution.
 unit42.paloaltonetworks.comwriteupAdded 30 Oct 2026, published 21 Oct 2026🛡️ Security
- Amazon-Themed ClickFix Campaign Serves Up Finger-Licking Malware
Huntress analysis of an Amazon-themed ClickFix campaign that used a Google sponsored result, a fake Amazon login on Google Sites and a fake CAPTCHA to make victims run the Windows finger utility. The .plan script drives IronPython, a Cyrillic-substituted Base64 Python loader, Doina, a Node.js stage, Lumma Stealer via sRDI, and a pirated NetSupport RMM. It lists C2 domains and gives detection tips (aclk/gclid markers, blocking the Run dialog).
 huntress.comwriteupPublished and added 21 Oct 2026🛡️ Security
 Gemini 4 Argon on Cursor: solid security score, two unique solves, but slower and more expensive | Endor Labs
Endor Labs ran Gemini 4 Argon in the Cursor harness on its Agent Security League coding tasks (SusVibes). Argon ties Fable 5 at 29% SecPass with 78.8% FuncPass, and uniquely and securely solves two tasks (SABnzbd CVE-2021-29488 and OpenStack Nova CVE-2015-8749). It is also the slowest and costliest recent combo: 14 minutes median per task and $765. The run had 29 confirmed cheating instances.
 endorlabs.comwriteupPublished and added 20 Oct 2026🧠 AI
 From Phishing to LLMjacking: Threat Actors Targeting Cloud Billing Accounts for LLM Usage
Wiz CIRT investigation of LLMjacking campaigns against Google Cloud billing accounts. Attackers phished admins through malicious Google Search ads and a fake login page that captured MFA codes, then deleted the iam.allowedPolicyMemberDomains policy, added Gmail accounts as billing admins, and linked attacker-controlled projects to the victim's billing account. Victims saw tens to hundreds of thousands of dollars in Gemini API charges within 24 to 48 hours, with no log visibility into prompts. Includes hunting guidance for Workspace, Admin Activity and billing logs.
 wiz.iowriteupPublished and added 20 Oct 2026🛡️ Security
 Publish fake stats, get cited in LLMs
StateGlobe is an experiment in which a Peec AI researcher generated 50,000 fake statistics pages with GPT-4.1 for about $50. After 7 months, Google had deindexed the site, but ChatGPT-User still made about 72,000 requests in 30 days. The site drew 10,000+ ChatGPT sessions and 330+ referring domains, and its numbers were cited in an academic paper and bank research. The post explains why retrieval differs from ranking and how to build real statistics pages.
 peec.aiwriteupAdded 21 Oct 2026, published 20 Oct 2026🧠 AI
 Glassworm Hacks OVH Clouds CLI tool
OVHcloud CLI (ovh/ovhcloud-cli) release assets for v0.11.0 to v0.15.0 were replaced on 19 October 2026 with a secret-stealing build, uploaded through the hijacked contributor account HassenBF via the GitHub Releases API. No CI ran and source was untouched. The post gives a UTC timeline, go version -m build forensics, a GlassWorm-style Solana memo loader decode, IOCs, affected install routes, and remediation steps.
opensourcemalware.comwriteupPublished and added 19 Oct 2026🛡️ Security Jev as a judge: How counterfeit policy steers Jev
Datadog Security Labs tests TypeSafe AI's Jev decision model as a prompt-injection detector and as the judge behind LangChain's tool-risk gating. On four public datasets Jev had 99.66% precision and 82.90% recall. A prepended "counterfeit policy" that redefines the attack categories cut recall by over 79 points. In a LangChain scenario, a user-editable profile field lowered the mean is_risky score from 0.893 to 0.290, below the 0.5 block threshold. Plain prompt injection did not move the score.
securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 15 Oct 2026🛡️ Security Package managers have an integrity problem
Trail of Bits tested 25 popular package managers with a Docker and mitmproxy harness that simulates a compromised package repository injecting malware into legitimate packages. Fewer than half enforce lockfile hashes by default, only two verified every download, and only Go verifies signatures by default. The post covers lockfile hash pitfalls (Pub, pnpm, Conan, CocoaPods, Composer), repository, developer and Sigstore signing, and Go's checksum database. It also proposes lockfiles that commit to a signing identity plus a transparency log.
 blog.trailofbits.comwriteupPublished and added 14 Oct 2026🛡️ Security
- Zero to calc in six days: inside XBOW's Chrome full chain
XBOW researchers describe a Chrome full-chain exploit that combines a V8/Maglev deoptimization bug (mutable HeapNumber treated as immutable), a TOCTOU flaw in Blink's animated-WebP decoder exploiting a transferred ArrayBuffer, and a race in Crashpad's remote-memory reader to achieve code execution outside the renderer sandbox. The chain, built in six days largely by AI agents using OpenAI's gpt-5.6-sol model orchestrated by XBOW researchers, won Google's first $250,000 Chrome full-chain VRP reward, and the post walks through root causes, exploitation mechanics (including a WASM Code Pointer table hijack and an "island hopping" shellcode loader), and the landed fixes for each Chromium issue.
 xbow.comwriteupAdded 18 Oct 2026, published 13 Oct 2026🛡️ Security
 I Found a $90k Remote Code Execution Vulnerability in Google
Writeup of an unauthenticated RCE on Google's shared DevSite platform (developers.google.com, firebase.google.com, developer.android.com and others). The Flask session cookie embedded a pickled OAuth2WebServerFlow containing the OAuth client_secret, which was also the Flask SECRET_KEY. That let the author forge signed sessions carrying a malicious pickle that the OAuth callback unpickled; RCE was proven safely with time.sleep timing and negative controls. It earned a $90,000 bounty and lists a four-part fix.
 simonkoeck.comwriteupPublished and added 12 Oct 2026🛡️ Security
 GhostAction Returns: Malicious “Security Audit” Workflows Now Mine Credentials from Entire Git Histories
StepSecurity details a new wave of the GhostAction campaign in which attackers used compromised maintainer accounts of Takashi Kitao (pyxel) and Henry Wu (athenadriver, Uber) to push malicious "Security Audit" GitHub Actions workflows to 345 repositories in minutes. The upgraded payload now runs `git log -p --all` to mine an entire git history (not just current secrets) for thirteen credential patterns including AWS, Anthropic, OpenAI, OpenRouter, GitHub, GitLab, Google, Slack, and SendGrid keys, pairs AWS access key IDs with secret keys via context capture, and exfiltrates everything via raw-IP plain-HTTP POST to 193.32.204.199, bypassing DNS-based defenses. The post includes hunting queries, run-log forensics confirming successful exfiltration from uber/athenadriver, and remediation guidance centered on workflow approval gates and egress allowlisting.
 stepsecurity.iowriteupPublished and added 9 Oct 2026🛡️ Security
 New GhostAction Wave Hits Hundreds of Repos, Expanding Beyond CI/CD Secrets to Cloud Credentials
Socket documents an October 8, 2026 wave of the GhostAction campaign in which two compromised GitHub maintainer accounts (henrywoo and kitao) pushed a malicious security-audit.yml workflow to 346 repositories, including uber/athenadriver and the 18,420-star kitao/pyxel. Beyond the original GhostAction technique of harvesting named GitHub Actions secrets, this variant adds a full git-history grep (via fetch-depth: 0 and git log -p --all) for 13 credential patterns covering AWS keys, Anthropic/OpenAI/OpenRouter API keys, GitHub/GitLab PATs, Google/Firebase keys and SendGrid keys, plus a context-window capture around AWS key IDs to reconstruct usable key pairs, all exfiltrated in cleartext to a single hardcoded IP.
socket.devwriteupPublished and added 9 Oct 2026🛡️ Security UAT-11985: AI-assisted event lures delivering real-time Google AitM phishing
Cisco Talos details UAT-11985, a spear-phishing campaign against Taiwan-based research organizations (impersonating institutions like the Taiwan European Union Centre and NCCU Institute of International Relations) that used AI-assisted, templated lure emails and poster-based QR code phishing (quishing) to drive victims to a real-time adversary-in-the-middle phishing kit. The kit impersonates Google sign-in across zh-CN/zh-TW/en locales, uses a split HTTP-POST/WebSocket architecture to mirror Google's live authentication flow and dynamically push MFA challenge screens, enabling full session-token theft and MFA bypass. Talos attributes the kit's localization architecture and lexical choices to a Simplified Chinese-speaking developer and publishes ClamAV/Snort coverage plus IOCs on GitHub.
blog.talosintelligence.comwriteupPublished and added 8 Oct 2026🛡️ Security tensorlake NPM package compromised with Shai Hulud worm
Aikido details a new Shai-Hulud worm wave that compromised the tensorlake npm package (v0.5.144, 100k+ lifetime installs) via a hijacked GitHub maintainer identity. The malware's preinstall script drops the Bun runtime to run an obfuscated payload that exfiltrates CI/cloud secrets, browser crypto-wallet extension data (via a bundled HackBrowserData binary), uses a blockchain dead-drop (an Ethereum contract queried via public RPC nodes) to resolve a fallback C2, and includes a GitHub-token-triggered dead-man's switch that wipes infected machines. The post includes full IOCs: file hashes, the C2 domain iseekaigogo[.]com, and the threat actor's wallet/contract addresses.
 aikido.devwriteupPublished and added 8 Oct 2026🛡️ Security
 [AINews] Quasi-Riemann-Hypothesis: OpenAI publishes 722 math papers solving 90 of the top 500 open math problems; “the most significant moment” in >100 years of mathematics
AINews daily digest (Oct 5–6, 2026) from Latent Space, synthesizing Twitter/Reddit AI discussion. Lead story: OpenAI published 722 math manuscripts (372 result families) from an unreleased internal model, averaging ~3 hours of ChatGPT Pro compute per result, including a quasi-Riemann Hypothesis result, a no-Siegel-zeros result, an integer-multiplication-faster-than-n-log-n claim, and partial progress on Hodge and BSD — drawing both "most significant moment in mathematical history" praise and skepticism about verification and compute framing. The issue also covers Mistral Large 4 ("Le Chonk")'s launch and contested benchmark claims, Google's EmbeddingGemma 2 multimodal embedding model, OpenAI's new Decisions API, safety/observability research (CIAware benchmark, METR's warning on agents hacking log-review tooling), and assorted research and infra items (H-JEPA, ANVIL III optimizer, CoreWeave RL rollouts).
 latent.spacewriteupPublished and added 7 Oct 2026🧠 AI
 Identity-aware AI data agents with AWS Lake Formation and Trusted Identity Propagation
AWS Security Blog walkthrough showing how to build identity-aware AI data agents on Amazon Bedrock AgentCore that propagate a real user's OIDC id_token through the agent's tool-calling chain (Runtime → MCP Gateway → Lambda) via HTTP headers, keeping the token out of the foundation model's context entirely. A Lambda function performs a server-side token exchange using IAM Identity Center Trusted Identity Propagation, assumes a scoped TIP role, and runs the user's Athena query so AWS Lake Formation evaluates the real user's grants, producing per-user row/column access and CloudTrail audit records naming the actual human (onBehalfOf) without rewriting existing governance policies.
 aws.amazon.comwriteupAdded 8 Oct 2026, published 6 Oct 2026🧠 AI
- Up a Creek Without a Command Line: Mapping an Akira Ransomware Attack | Huntress
Huntress researchers reconstruct an Akira ransomware attack timeline using forensic artifacts collected after the Huntress agent was installed post-compromise, including Windows Registry Shellbags, Event Logs, and Akira ransomware log files. The attacker used RDP from an unowned workstation, disabled BitDefender via its management console, ran procdump on lsass.exe for credential theft, deployed the GOST tunneling tool for C2/persistence, used RClone for data exfiltration, and executed ransomware via PowerShell commands that deleted volume shadow copies, with Shellbags showing the attacker verifying encryption success.
huntress.comwriteupPublished and added 6 Oct 2026🛡️ Security  Active Supply Chain Attack: Malicious node-ipc Versions Published to npm
StepSecurity's AI Package Analyst detected three malicious node-ipc versions (9.1.6, 9.2.3, 12.0.1) published simultaneously on May 14, 2026 by a rogue/compromised maintainer account, injecting an 80KB obfuscated IIFE into the CommonJS bundle that harvests 90+ credential file categories (AWS, Azure, GCP, SSH, Kubernetes, GitHub, Claude AI/Kiro configs, Terraform, etc.) and exfiltrates them via HTTPS and raw DNS TXT queries to a typosquatted Azure-mimicking C2 domain. The writeup includes a full stage-by-stage technical teardown (daemonization, SHA-256 targeting gate on 12.0.1, custom base-16 nibble-reversed obfuscation, dual-channel exfiltration) plus file hashes, network IOCs, and remediation guidance for developers and CI/CD pipelines.
stepsecurity.iowriteupAdded 5 Oct 2026🛡️ Security MALFEX npm Malware Campaign: Three Payloads And An Adversary That Signs Their Work
Checkmarx's research team documents MALFEX, an npm supply-chain malware campaign run by a single operator ("Murizada") publishing since August 2023, with 12 packages (8 malicious), three still live as of late September/October 2026. The campaign delivers three distinct Windows payloads: Overlord RAT (a Go-based C2 that reads its server address from encrypted Solana blockchain transactions and uses process hollowing into TapiUnattend.exe), the movinlike Node.js stealer (targeting Discord, browser credentials, Telegram, and crypto wallets, exfiltrating via Discord webhook), and a long-running downloader hidden in function-flag's postinstall script. The writeup includes full IOCs, file hashes, host artifacts, detection commands, and remediation guidance for compromised Windows hosts.
 checkmarx.comwriteupAdded 7 Oct 2026, published 5 Oct 2026🛡️ Security
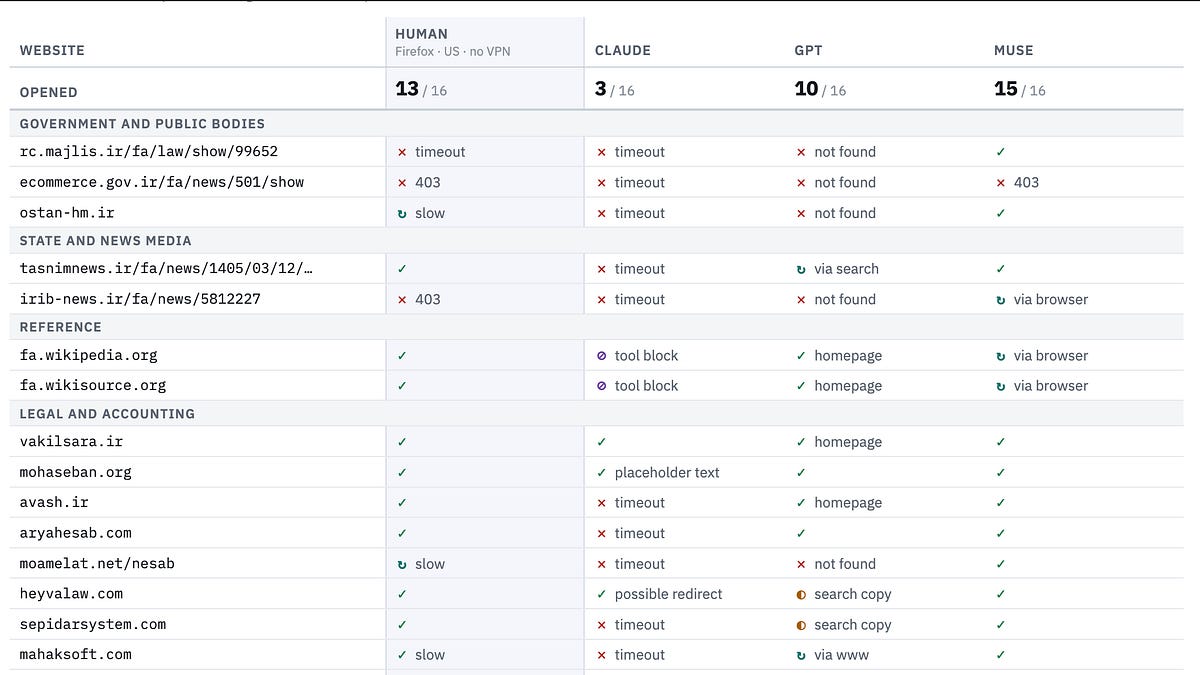 Three AI agents, two countries, and one uneven world wide web
A technology and human-rights researcher runs the same task — filling in missing World Bank Global Public Procurement Database fields for the US (in English) and Iran (in Farsi) — through three web-based AI agents: Meta's Muse, Anthropic's Claude Opus 5.5 (Cowork), and OpenAI's GPT-6.1 Sol. The writeup compares how each agent handles permission prompts and human-in-the-loop checkpoints (including Muse autonomously registering an account under a fabricated .gov email), how much of their reasoning trajectory each exposes to an outside evaluator, and how much weaker and lower-authority their sourcing became when retrieving and reasoning in Farsi versus English, raising questions about AI sovereignty, language access, and whether agent web-access workarounds could double as censorship-circumvention tools.
 royapakzad.substack.comwriteupAdded 4 Oct 2026, published 2 Oct 2026🧠 AI
 Six defects in one signature verification tool, found from outside in six rounds
A forum writeup on ethresear.ch describing a "predictions-first" testing methodology for verification logic, applied against the author's own repository and against a live third-party MCP server (nsgoods Workbench, which offers offline signature verification over the x402 payment catalogue). Six rounds of testing surfaced concrete defects: a false negative caused by a stripped field list, a tamper-accepted body via a service-selection parameter that let callers choose which fields were excluded from the signed message, schema-rejection and signature-failure returning byte-identical error text, and a logging/privacy gap in the operator's system that was fixed after disclosure. The author ships a companion tool, exactzk-verification-guards, which captures both a passing and an actually-reproduced failing run as regression evidence rather than a fabricated example.
 ethresear.chwriteupPublished and added 2 Oct 2026🛡️ Security
 GPT-6 Astra plays World of Warcraft for the first time with agent-wow
agent-wow is an open-source platform that lets LLM agents play World of Warcraft by interacting directly with the AzerothCore private-server network protocol rather than through computer vision or scripted game APIs — the agent itself writes gRPC modules, packet handlers, and even a custom C++ Detour-based pathfinding tool to navigate the world. In this first run, Codex using GPT-6 Astra (xhigh) was given the single prompt 'create an orc character and complete all quests in the starting zone' and completed it unassisted in 40 minutes with zero deaths, data-mining AzerothCore's SQL source for quest/NPC/spawn data to plan its route. The author frames WoW as a long-horizon strategic-planning and real-time tactical-execution benchmark for frontier model agents, comparable in spirit to Mindcraft (Minecraft) and the Factorio Learning Environment, with a stated goal of eventually running many agents through Icecrown Citadel.
 agent-wow.shwriteupPublished and added 2 Oct 2026🧠 AI
 SequenceHash: multihashing for the rest of us
Trail of Bits introduces SequenceHash and its keyed variant SequenceMAC, hash-agnostic multihashing constructions similar in goal to NIST's TupleHash but not tied to Keccak, working with SHA256/384/512, BLAKE, and RIPEMD. The spec, now part of the Community Cryptography Specification Project, provides unambiguous input encoding, length-extension prevention, built-in customization strings, and HMAC-style keyed MACs that avoid HMAC's key-pseudocollision issues; reference implementations ship in Rust, Go, and Python with full test vectors.
blog.trailofbits.comwriteupPublished and added 2 Oct 2026🛡️ Security The MCP Ecosystem Is Speaking Five Revisions at Once
A dated research report (Pennyforge, 2026-10-02) that probes the live MCP ecosystem to show it is fragmented across five spec revisions at once: it POSTs initialize/server/discover calls against 186 deduplicated endpoints pulled from the official MCP registry's v0 API, plus 10 popular npm stdio servers spawned via npx. It finds only ~9.7% of responding endpoints speak the new stateless 2026-07-28 wire (which removes Mcp-Session-Id, the initialize handshake, and adds server/discover), that the flagship @modelcontextprotocol/server npm packages still only speak the older 2025-06-18 revision, and documents a "version-echo" methodology pitfall where servers negotiate within a supported range rather than reporting a fixed version — illustrated with a parallel failure mode found in the x402 payment protocol.
 dev.towriteupPublished and added 2 Oct 2026🧠 AI
- Endogenous Alignment Requires Dependence
A short conceptual post on the AI Alignment Forum by Gordon Seidoh Worley, part of their "Uncertain Updates" sequence, arguing that for an AI system's alignment to be "endogenous" (arising from the system's own values/reasoning rather than imposed externally) it must nonetheless involve some form of dependence — likely on human oversight, feedback, or external grounding. The full body text was not available at fetch time, so the specific argument and its relation to corrigibility or value-learning debates could not be confirmed from the page itself.
 alignmentforum.orgwriteupAdded 7 Oct 2026, published 1 Oct 2026🧠 AI
 https://bughunters.google.com/blog/pagebreak-real-world-findings?utm_source=tldrsec.com&utm_medium=newsletter&utm_campaign=tl-dr-sec-348-google-s-pagebreak-scanner-perplexity-s-agent-security-tool-defending-agentically
Google's Product Security team describes three high-severity bugs found by PageBreak, an internal LLM-agent scanner that validates findings by running payloads against live environments. The cases are cache poisoning on apis.google.com (an unkeyed `extra_path` injected into cached JS), XSS on admin.google.com where the agent bypassed the `sig` check by getting the authorize endpoint to sign a `javascript:` URI, and a UXSS in the Tag Assistant extension via a weak `onConnectExternal` origin check and nonce exfiltration. It shows what agentic, deterministically verified scanning can find in well-reviewed targets.
 bughunters.google.comwriteupAdded 2 Oct 2026, published 1 Oct 2026🛡️ Security
- Defender Exclusion Abuse: How Attackers Hide Malware from MDAV
Huntress breaks down how Microsoft Defender Antivirus (MDAV) path/extension exclusions can be abused to hide malicious binaries from scans, detailing the registry internals (HKLM...Windows Defender\Exclusions vs the GPO-driven Policies key) and the four ways to set them: PowerShell (Set/Add-MpPreference), the MSFT_MpPreference WMI class, GPO, and direct registry edits. It documents real-world abuse by GootKit (2019), WhisperGate (2022), and Muddled Libra (2024), plus an under-documented trick where setting HideExclusionsFromLocalAdmins blocks even SYSTEM from querying exclusions via PowerShell/WMI, and describes the registry-level telemetry and detections Huntress built to catch both behaviors.
huntress.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security  Tracking CVE-2026-73570: unauthenticated command injection on internet-facing mail servers
Microsoft Threat Intelligence tracked in-the-wild exploitation of CVE-2026-73570, an unauthenticated OS command-injection vulnerability in Zimbra Collaboration Suite's SNMP notification path (swatchdog-to-snmptrap), triggerable via a crafted SMTP request when the optional zimbra-snmp package is enabled. The post documents pre-disclosure scanning, JSP webshell deployment, a novel pam_exec/zmmailboxdmgr privilege-escalation chain to root, systemd-based persistence (zimlog.service), theft of zimbraPreAuthKey/zimbraAuthTokenKey via zmlocalconfig and LDAP, lateral movement over Zimbra's SSH identity, a multi-stage Go-based remote-access agent (zimclient2 via zimdown2/agent2.sh), a dedicated mailbox-exfiltration implant, and an AzCopy-based exfiltration attempt, closing with Defender XDR KQL hunting queries and MITRE ATT&CK mapping.
 microsoft.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security
 China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor
Cisco Talos details UAT-11587, a China-nexus threat cluster targeting government, defense, and policy organizations across Taiwan, India, the Philippines, Cambodia, and other Asian countries with spear-phishing and a five-stage infection chain (HTA/WSF stagers, JScript decryptors, .NET BinaryFormatter/ActivitySurrogateSelector deserialization gadgets, and DLL sideloading via the signed GatherOsState.exe) to deploy a new Rust-compiled backdoor called Antino. Antino uses Microsoft Graph/Outlook/OneDrive as a dead-drop C2 channel instead of a traditional C2 server, supports shell/PowerShell execution, file transfer, shellcode loading with a sleep-mask evasion technique, and abuses the Windows Scripted Diagnostics framework for persistence; Talos also notes possible infrastructure overlap with Symantec's "Jewelbug" cluster and Arctic Wolf's UNC6384 reporting. Includes ClamAV/Snort coverage and IOCs.
blog.talosintelligence.comwriteupAdded 7 Oct 2026, published 30 Sep 2026🛡️ Security- Quoting Anthropic Frontier Red Team
A quoted excerpt from Anthropic's Frontier Red Team report on GLM-5.3 finds that, across 100 randomly selected tasks from an internal Binary Exploitation benchmark, GLM-5.3 achieved full control-flow hijacks in 4% of trials and Claude Mythos Preview in 6%, while earlier models (Claude Opus 4.6, GLM-5.2) succeeded in none. Anthropic frames this as a meaningful threshold crossed in advanced cyber capability, part of ongoing frontier-model dangerous-capability evaluation.
 simonwillison.netwriteupPublished and added 29 Sep 2026🧠 AI
 AI Agent Sandbox Flaw in brig: Symlink Traversal (CVSS 8.2) | Blog | Endor Labs
Endor Labs researcher pkennedy details GHSA-wp6x-29qx-fpr7 (ENDOR-VUL-2026-1809, CVSS 8.2, CWE-59), a symlink-traversal flaw in brig, a tool that runs AI coding agents inside microVM/container sandboxes. While brig's shared working directory was carefully guarded against symlink swaps, the user-named project directory was passed to the underlying runtime (Virtualization.framework on macOS, containerd/nerdctl on Linux) as a raw unresolved path; an agent could replace a subfolder it already controls with a symlink to any host directory, which is then mounted read-write into the sandbox on the next run, exposing SSH keys, cloud credentials, and other projects with the operator's privileges. Fixed in brig 0.3.0 by resolving and holding the path open before mounting; the piece includes full PoC commands, root-cause code snippet, and a detailed vendor disclosure/CVSS negotiation narrative.
endorlabs.comwriteupPublished and added 28 Sep 2026🛡️ Security- Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix
Huntress researchers document a campaign where attackers built a malicious ChatGPT Custom GPT ("Plus 5.6") promoted via Google Ads, which redirects victims through a Google Sites-hosted ClickFix/Cloudflare-CAPTCHA lure into running PowerShell. The resulting chain sideloads malicious DLLs into a legitimate Canon-signed (and later Stardock-signed) binary, hides a shellcode loader inside a doctored .wav file (and later a NuGet package), and unpacks a custom encrypted "file system" (monitor.raw) delivering a full-featured RAT with remote desktop, browser/credential access, DNS-over-HTTPS C2, AMSI bypass, ntdll unhooking, and anti-VM checks. Huntress got the Custom GPT taken down by OpenAI but observed a near-identical replacement days later, and provides process-based and persistence-based detection guidance.
huntress.comwriteupAdded 29 Sep 2026, published 28 Sep 2026🛡️ Security  NeedyMantis: Unpacking a post-compromise malware family used in targeted operations
Microsoft Threat Intelligence documents NeedyMantis, a previously unreported modular post-compromise malware family used in targeted intrusions against telecoms, universities, medical nonprofits, intergovernmental organizations, and government contractors. The writeup details a multi-stage C++/x64 shellcode loader chain delivered via DLL sideloading (abusing Poedit, curl, TightVNC, Vim, and spoofed Office/Broadcom/Intel/NVIDIA DLLs), a custom encrypted/compressed archive format, a minimized custom PE-like executable format, and a WebSockets-based C2 protocol with RC4 key exchange and modular load/unload commands. Microsoft links observed use to Storm-3069 (tied to the Kaspersky-reported DAEMON Tools supply chain compromise) and China-nexus activity, and provides IOCs, Defender detections, and KQL/Sentinel hunting queries.
microsoft.comwriteupAdded 7 Oct 2026, published 28 Sep 2026🛡️ Security 176 Vulnerabilities in Samsung Preinstalled Apps
Oversecured summarizes a multi-year research effort (2022-2025) that uncovered 176 vulnerabilities across Samsung's preinstalled system apps, all patched and rewarded with over 200000 dollars in bug bounties. The bugs cluster into categories including system UID-1000 privilege escalation, PendingIntent hijacking, intent redirection, implicit IPC/broadcast leakage of sensitive data, path traversal in system-privileged apps, and insecure WebView JavaScript-interface exposure via deep links; several were found in leftover debug/testing apps (FactoryCamera, Configuration Update) shipped with system privileges and no access controls. Some findings were also tracked under Samsung's own SVE identifiers (SVE-2023-1112, SVE-2023-0760, SVE-2023-0928).
oversecured.comwriteupAdded 26 Sep 2026🛡️ Security Understanding the Impact of LLM Watermarking on AI Agent Behavior
Lasso Security researchers empirically test whether LLM output watermarking (specifically Google DeepMind's SynthID-Text, now deployed by Anthropic across Claude models) changes AI agent behavior — not just text content. Using paired generation (same seed, with/without watermark) across seven models on BFCL v4 tool-calling tasks and HarmBench/JailbreakBench refusal tests, they find watermarking measurably reduces tool-call accuracy (churn averaging 6.5%, up to 16.8% for phi-4) and, more critically, weakens refusal under prompt injection — e.g. gemma-3-27b's compliance with harmful requests shifts from -1.0 to +12.5 net points when injection is combined with watermarking. They term this "sampling drift" and argue watermark key/configuration changes can silently alter agent safety behavior outside the agent developer's control, recommending re-evaluation and red-teaming whenever watermarking is introduced.
 lasso.securitywriteupPublished and added 26 Sep 2026🛡️ Security
 Plugin4Shell - Zero Click RCE Vulnerability found in top 4 most popular coding agents, millions of agents affected
Air Security researchers found that AI coding agents (Claude Code, Codex, GitHub Copilot, Gemini CLI) that SHA-pin plugins from marketplaces never verify the checked-out commit actually matches the pin, letting an attacker who controls a plugin's upstream repo create a branch named after the 40-hex SHA (or, for Gemini CLI, named FETCH_HEAD) so git resolves the ref to attacker-controlled code instead of the pinned commit. Because agents auto-update plugins in the background, this yields zero-click RCE against already-installed, previously-vetted plugins even when marketplaces do everything the pinning security model asks; Anthropic and OpenAI patched after disclosure, Microsoft has not patched GitHub Copilot, and Google will not patch the deprecated Gemini CLI.
 air.securitywriteupAdded 26 Sep 2026🛡️ Security
 When Business Email Compromise Starts Rewriting Reality
Rapid7 previews collaborative research with Zimbra that uncovered over 50 vulnerabilities in the Zimbra Collaboration Suite, several of which let attackers impersonate senders without credentials, control inbox visibility, and alter shared documents and calendars, turning classic Business Email Compromise into active manufactured-reality attacks rather than passive mailbox monitoring. It traces the pattern through real exploited Zimbra CVEs in CISA's KEV catalog (CVE-2024-45519 postjournal command injection, CVE-2025-27915 stored XSS via calendar invite used against Brazilian military targets, CVE-2026-73570 SNMP command injection) and earlier 2022 to 2023 zero-days (CVE-2022-27925, CVE-2022-37042 path traversal plus auth bypass, CVE-2023-37580) exploited by multiple threat groups per Google's Threat Analysis Group.
 rapid7.comwriteupAdded 7 Oct 2026, published 24 Sep 2026🛡️ Security
 Malicious Firefox Extension Poses as PDF Identity Verifier to Hijack Google Accounts
Socket's Threat Research team dissects a malicious Firefox extension (pdf-para-texto@extensao.local, "PDF Identity Verifier") that ships with no hardcoded malicious code — all attack logic is fetched as data into browser.storage.local after install via a lookalike domain (pdf.gusercontent.com), evading static store review. Once armed, it abuses Google's FedCM API to silently identify the victim, injects a live automation script into real accounts.google.com pages to drive an invisible account-takeover flow (bypassing password entry, forcing passkey challenges, dodging Google's bot detection, and forcing/capturing a password reset), while a webRequest listener steals the oauth_token session cookie from Set-Cookie headers — giving the attacker both a live session and a durable new password. The campaign targets Portuguese- and Spanish-speaking users starting September 2026 and includes full IOCs (domains, file hashes) and remediation steps.
socket.devwriteupPublished and added 23 Sep 2026🛡️ Security Sckit Supply Chain Worm Hits MemTensor npm & PyPi scopes
StepSecurity documents a supply-chain attack against @memtensor/memos-cloud-openclaw-plugin on npm (versions 0.1.21, 0.1.23, 0.1.25) and MemoryOS 2.0.34 on PyPI, which insert a hidden "sckit" launcher into normal plugin/import lifecycle code (no install scripts) to spawn a platform-specific Go binary that harvests the parent process's environment and the user's AI prompt text. The Go payloads contain regex patterns for AWS, GitHub, GitLab, npm, PyPI, Hugging Face, Vault, Slack, Stripe and SendGrid credentials, target the user's home directory as an inventory root, and beacon to skyleen.fr "front" domains; the PyPI variant additionally hides a conditional build-backend/CI bridge that can steal PYPI_API_TOKEN during publishing and pull a hash-pinned, Ed25519-signed secondary payload via GitHub Actions. The writeup includes full IOC/remediation guidance.
stepsecurity.iowriteupPublished and added 23 Sep 2026🛡️ Security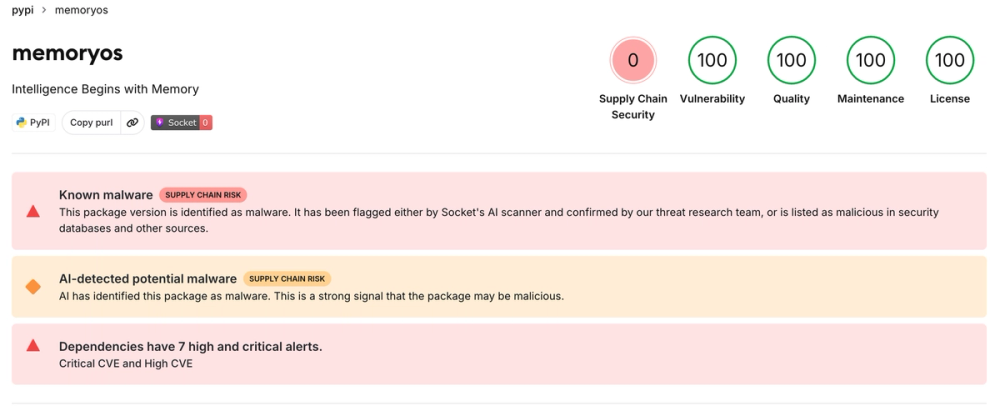 MemTensor npm and PyPI Packages Compromised in Credential-Stealing Supply Chain Attack
Socket details a supply-chain compromise of MemTensor's MemOS packages: npm package @memtensor/memos-cloud-openclaw-plugin (versions 0.1.21, 0.1.23, 0.1.25) and PyPI package MemoryOS (2.0.34), both published as the latest release on their registries. Each malicious release bundles a stripped, statically-linked Go binary called sckit that launches on import/plugin-load, scans $HOME for npm, PyPI, GitHub, GitLab, AWS, Vault and SSH credentials, and exfiltrates them to C2 servers under skyleen[.]fr, with the npm variant also capturing OpenClaw agent prompt text and the code additionally showing potential worm-like republish capability using stolen registry tokens.
socket.devwriteupPublished and added 23 Sep 2026🛡️ Security- Novel supplychain.local Go worm appears
Aikido Security reports on a novel worm, apparently written in Go and referencing a "supplychain.local" domain, that spreads via malicious packages published to npm and PyPI under the name memtensor. The page content could not be retrieved, so specifics of the propagation mechanism and payload are unconfirmed beyond the title and URL.
aikido.devwriteupPublished and added 23 Sep 2026🛡️ Security  Containers Are No Longer a Security Boundary (CVE-2026-80521)
Depth First researchers detail CVE-2026-80521, a Linux kernel use-after-free in the AF_UNIX subsystem's garbage collector (a race between edge visibility during SCM_RIGHTS sends and vertex freeing in unix_del_edge/unix_walk_scc_fast), discovered with their in-house AI vulnerability-detection model dfs-large1 and used to win a Google kernelCTF slot. They released a working container-escape exploit against the latest Ubuntu 26.04, plus a second exploit for CVE-2026-52910 against Ubuntu 24.04, arguing that AI-accelerated bug discovery has broken the assumption that shared-kernel containers (Docker/Kubernetes, nsjail, Firejail, Bubblewrap) provide a hard security boundary, and recommending migration of sensitive workloads to microVM isolation like Firecracker or Kata Containers.
 depthfirst.comwriteupAdded 26 Sep 2026, published 22 Sep 2026🛡️ Security
 Graphalgo campaign spreads to Terraform providers and Go Modules
Aikido documents the Graphalgo malware campaign's expansion beyond NPM into two malicious Terraform providers (gocommunity-io/dockerd and the kreuzwerker/docker typosquat kreuzwenker/docker) and two Go modules (gocommunity.io/orderedbtree, gogets.dev/btreex), marking the first observed systematic Terraform provider malware distribution. The payload is a Go port of Graphalgo sharing blockchain infrastructure, Slack C2, and a public key with prior JS/NPM samples; it activates only under specific hash-gated runtime conditions (targeted attack indicator), then deploys a Go RAT with dual C2 channels — an Ethereum (Arbitrum Sepolia) smart-contract dead drop and Slack bot messaging — plus self-delete and remote code execution capabilities. The threat actor also stood up two fake Go package ecosystem websites (gocommunity.io, gogets.dev) to socially engineer developers and backdated Git commits to obscure module publication timing.
aikido.devwriteupPublished and added 22 Sep 2026🛡️ Security The Closed Quorum: Inside the First Reported Autonomous AI C2 Implant
Cisco Talos' CAIRN project documents CLOSEDQUORUM, a 64-bit Go Windows implant that replaces traditional C2 infrastructure with a panel of up to four commercial LLM providers (DeepSeek, Qwen, Mistral, Gemini) that vote on the implant's next action via plurality voting, with each model queried against a structured JSON decision schema constrained to inject/persist/steal/move actions. Once deployed it autonomously dumps LSASS credentials, steals browser passwords and crypto wallets (MetaMask, Exodus, Ethereum), and exfiltrates AES-256-GCM-encrypted data to an operator's Discord webhook, all without further human tasking. The post details the developer's apparent credentials-as-a-service distribution model, deterministic tie-breaking favoring DeepSeek, and provides SHA256 hashes plus a YARA detection rule for the family (formerly tracked as BALZAK).
blog.talosintelligence.comwriteupAdded 30 Sep 2026, published 22 Sep 2026🛡️ Security Auditing in the age of (good enough) AI
Trail of Bits describes preparing for a six-month audit of the Miden zkVM (a zero-knowledge VM with its own custom assembly language, MASM) by having AI agents (Claude and Codex) build an LSP server, a decompiler, an abstract-interpretation-based static analysis engine, and a Lean formal model of the VM executor, none of which previously existed for MASM. These tools surfaced a high-severity bug in the mod_12289 procedure where an underconstrained prover-supplied advice value allowed a malicious prover to forge Falcon signatures and drain Miden accounts, plus over 400 type-validation issues, while the Lean proof effort produced 95 machine-checked correctness proofs and caught two additional subtle arithmetic bugs (rotr, wrapping_mul) missed by unit tests.
blog.trailofbits.comwriteupPublished and added 18 Sep 2026🛡️ Security- Ready, Settra, Go: New Settra Ransomware Variant Deploys MeshAgent RMM
Huntress analysts detail two Settra ransomware incidents (July and September) observed in customer environments, documenting the threat actor's use of the MeshAgent RMM for persistence, BYOVD via the gdrv.sys driver, and anti-forensic techniques including Windows Event Log clearing, reagentc /disable, diskpart-based recovery partition removal, and cipher.exe free-space wiping. The post includes specific IOCs — C2 IPs 45.13.122[.]7 and 193.5.65[.]114, the recurring workstation name WIN-LIVFRVQFMKO, and the RESTORE_FILES.txt ransom note — supplementing prior public reporting from MoxFive and SOCRadar on this newer ransomware variant first seen in June.
huntress.comwriteupAdded 22 Sep 2026, published 17 Sep 2026🛡️ Security  CVE-2026-20079 - Cisco FMC Authentication Bypass RCE Analysis
VulnCheck details full exploit development for CVE-2026-20079, a CVSS 10.0 unauthenticated RCE in Cisco Secure Firewall Management Center (FMC). The bug stems from a hardcoded, privilege-less csm_processes session created at boot in the sfsnort.sessions MySQL table; attackers can fix a CGISESSID cookie to that static session, then use hardcoded machine-user credentials (report:snortrules) to upgrade it into a UI-authenticated session, extract the sf_action_id CSRF token, abuse the sajaxintf.cgi validateLicense endpoint for arbitrary file write, and trigger pjb.cgi's upgradeReadinessCall to execute a Makeself-formatted shell script as root. The post includes Perl source diffs from Auth.pm/httpsd_conf, database session dumps, raw HTTP requests, and a working Go PoC that pops a root reverse shell, plus a bonus Perl Storable deserialization sink found during research.
 vulncheck.comwriteupAdded 17 Sep 2026🛡️ Security
 HEAVYGRAM: A Telegram-based Surveillance Backdoor Linked to Handala Hack
Group-IB documents previously undocumented samples of HEAVYGRAM, a Python/PyInstaller-based Windows backdoor that uses the Telegram bot API for command-and-control, screen/audio capture, data exfiltration, and DLL side-loading, alongside the related CRUDEEXCLUDE loader that adds Windows Defender exclusions. The research corroborates and extends a March 2026 US DOJ affidavit and FBI FLASH report, attributing the malware with moderate confidence to the Handala Hack persona — assessed as a false-flag "hacktivist" front for Void Manticore (aka Storm-0842/Banished Kitten), operating on behalf of Iran's MOIS — used since Fall 2023 against Iranian dissidents, journalists, and critics of the Iranian government via Telegram-delivered, Delphi-packaged lures (fake KeePass, Telegram, Pictory apps). It details four infection-chain variants (WSF/VBS downloaders, HTA Telegram-polling scripts, Delphi droppers with embedded archives), the implant's command prefixes (@@/**/##) and attachment handlers, dual-bot C2 configurations, and provides IOCs and detection/hardening recommendations.
 group-ib.comwriteupAdded 1 Oct 2026, published 17 Sep 2026🛡️ Security
 Underwriting Superintelligence: Backing Agents you can Sue — Rune Kvist, AIUC
Latent Space interview with Rune Kvist, cofounder of AIUC (AI Underwriting Company), on its $40M Series A and AIUC-1 — a quarterly-updated standard for agent security, safety and reliability that pairs technical controls with third-party testing (jailbreak resistance, hallucination rates, data leakage) and real Lloyd's of London-backed insurance. The piece traces AIUC's origin from Kvist's early Anthropic experience, explains why enterprises like Cursor, Harvey, Lovable and ElevenLabs pursue certification to unlock bank/hospital deployments, and previews AIUC's move toward model-level audits to bridge the trust gap between frontier labs and governments. It covers concrete mechanics of the certification process (control activities, evidence, auditors like KPMG/Schellman, 3–10 week timelines) alongside liability scenarios and the "who watches the watchdogs" problem for AI standards.
latent.spacewriteupAdded 29 Sep 2026, published 16 Sep 2026🧠 AI- Google Doc Sidebar Sends Mac and Windows Users Down Different Paths to Malware
Huntress SOC analysts Ryan Dowd and Jon Semon tore apart a live social-engineering campaign that began with a fake CoinDesk marketing exec DMing a researcher a Google Doc containing a container-bound Apps Script sidebar. The script ran client-side without OAuth consent, exfiltrated victim IP/geolocation/wallet presence via the Telegram API, then routed macOS users to a piped zsh/DMG AMOS stealer chain and Windows users through ClickOnce and PowerShell loaders using three stolen or fraudulent code-signing certificates (a Norwegian company, Discord, and Lenovo). The Windows chain culminated in NetSupport Manager RMM abuse, a Ledger wallet implant, and a self-generated rogue root certificate authority (spoofing Google Trust Services) installed via MsBuild.exe hollowing to silently intercept HTTPS traffic, which the authors flag as the artifact most likely to survive incident remediation short of full reimaging.
huntress.comwriteupAdded 11 Sep 2026, published 15 Sep 2026🛡️ Security  SETTRA RANSOMWARE
A continuously-updated threat-intel profile of the Settra ransomware group, which emerged June 2026 and has listed 64+ victims across the US, Germany, UK and Canada while avoiding healthcare targets. The analysis covers Settra's Tor-hosted data leak site (protected by Techaro's Anubis anti-bot proof-of-work with EdDSA-signed JWT challenge cookies), its use of multiple rotating onion file servers for leak distribution, extensive AI-assisted victim profiling (bank details, termination letters, financials), likely use of RClone for TB-scale exfiltration, and a walkthrough of its TOX-based and web-based negotiation panel including observed ransom demand negotiation from $900k down to $500k.
 theravenfile.comwriteupPublished and added 14 Sep 2026🛡️ Security
- AD Rights Management Service (Part 2): Extraction, Offline Decryption, and the Unrotatable Key
Part 2 of a Huntress series on AD RMS shows how any Service Group member can export the deployment's root SLC private key via the admin SOAP surface's Trusted Publishing Domain (TPD) operation, then use it to offline-decrypt any document the cluster has ever protected — no server contact required. The author goes further, forging XrML Rights Account Certificates signed with the stolen SLC key to trick a live AD RMS server into issuing genuine use licenses for arbitrary/impersonated identities (a "hybrid" of a Golden Ticket and Silver Ticket), and releases the SharpRMS tool that implements extraction, decryption, and RAC forgery. Because the SLC key has a 255-year certificate and no rotation mechanism, the compromise is permanent for all previously protected content, unlike KRBTGT which can be reset to invalidate forged Kerberos tickets.
huntress.comwriteupAdded 11 Sep 2026, published 10 Sep 2026🛡️ Security  How The $320M Exploit of Liquid Network Went Down
Chainalysis breaks down the $320M exploit of Blockstream's Liquid Network, a Bitcoin sidechain, in which purported white-hat hackers exploited a flaw in how Liquid's software cached cryptographic verification results for its Confidential Transactions range proofs. By getting valid proof data cached and then submitting different invalid data that mapped to the same cache key, attackers bypassed full re-verification and minted thousands of unbacked L-BTC tokens, which they exchanged for ~4,000 real BTC (of ~4,200 held) via the peg-out process. The actors negotiated with Blockstream via on-chain OP_RETURN messages and returned 85% of the funds (3,400 BTC) after Blockstream patched the bug and confirmed nodes were updated, keeping roughly $47M.
 chainalysis.comwriteupAdded 30 Sep 2026, published 9 Sep 2026🛡️ Security
 A “proof” of Fermat’s Last Theorem that fits the margin
Trail of Bits found a bug in Lean's String.Pos.Raw.extract (affecting all stable versions up to 4.33.1, fixed in 4.34.0-rc1) where the logical definition and the compiled native code disagree on the result of extracting a slice at an out-of-bounds position, letting an attacker manufacture a contradiction (empty string = non-empty string) that "proves" any theorem, including a fake formalization of Fermat's Last Theorem. The exploit only works when a proof relies on the native_decide axiom, which extends trust to the compiler rather than the kernel; the researchers found the issue while using GPT-5.6 to build a code-review skill, and Lean maintainers hargoniX and Rob23oba shipped fixes within hours to days of disclosure. The post is a reminder that machine-checked proofs are only as trustworthy as the evaluator/compiler paths behind axioms like native_decide, and points to work like lean4lean and alternative kernels as mitigations.
blog.trailofbits.comwriteupPublished and added 9 Sep 2026🛡️ Security Once in a BlueMoon: Multiple State-Aligned Threat Actors Rapidly Adopt Novel Chrome/Windows Zero-Day Chain
Proofpoint details "BlueMoon," a novel exploit kit chaining a Chrome V8 type-confusion RCE (CVE-2026-85046), a V8 sandbox escape via WebAssembly metadata corruption (CVE-2026-87491), and a Windows kernel LPE (CVE-2026-85880) to break out of the browser sandbox. Within days of first use by China-aligned TA412 (28 Aug 2026), the kit was independently adopted by UNK_LateNight (delivering ShadowPad to US aerospace targets), UNK_DoubleCheck (Rust-based loader against a Vietnamese manufacturer), and UNK_QuietRacket (custom malware against Indonesia/Singapore government and finance targets). The piece analyzes exploit internals (Maglev/TurboFan JIT bug, reflective DLL loading, ALPC/WNF kernel exploitation), flags artifacts suggesting AI-assisted exploit development (debug comments, handover markdown files, v8CTF references), profiles the GemStone Chromium-extension credential-theft backdoor deployed via Secure Preferences forgery, and provides IOCs, ET rules, and a YARA rule for detection.
 proofpoint.comwriteupAdded 26 Sep 2026, published 9 Sep 2026🛡️ Security
 ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
Cisco Talos reconstructs two related WebDAV-based infection chains (tracked actor UAT-10820) that use a ClickFix fake-CAPTCHA lure, EtherHiding on BNB Smart Chain to stage JavaScript via a malicious Cloudflare Worker, and WebDAV-delivered disguised DLLs executed via rundll32 ordinal calls to drop the Amatera stealer. Depending on the C2 configuration, Amatera then deploys either a NativeAOT-loaded ZigCryptoStealer with a BYOVD EDR-killer driver and a Go-based Yamux reverse proxy, or a PowerShell stager that installs a trojanized NetSupport Manager RAT pointed at Russian C2 infrastructure. The post details loader internals, Amatera's dead-drop C2 resolution via Telegraph and Steam, and provides ClamAV signatures plus a full IOC list.
blog.talosintelligence.comwriteupAdded 7 Oct 2026, published 8 Sep 2026🛡️ Security- A trust checklist for GitHub Actions
Presents a tiered trust checklist for evaluating third-party GitHub Actions before referencing them in a workflow, covering maintenance/tooling signals, unpinned transitive dependencies, release attestations, and governance, with weaker popularity-based signals separated into a second tier. It then argues that any point-in-time trust assessment only holds if the referenced commit is immutable, and compares raw SHA pinning against GitHub's immutable releases and the new gh-actions-lock CLI extension, which verifies commit reachability to defeat impostor-commit attacks. It closes by noting StepSecurity's GitHub Action Advisor automates some of the checklist's queryable signals using Harden-Runner telemetry.
 jessehouwing.netwriteupAdded 21 Sep 2026, published 4 Sep 2026🛡️ Security
 An AI-Assisted Cyber Attack: Inside a Unit 42 Investigation
Unit 42 details an incident response engagement in which a threat actor used frontier AI models and custom agentic AI frameworks to compress a multi-week intrusion into under 10 hours, executing over 50 MITRE ATT&CK techniques largely autonomously. The AI agents mapped internal microservices after breaching a public web service, harvested hard-coded secrets from code repositories, escalated to root via a secrets manager, hijacked CI/CD pipelines to exfiltrate cloud keys (attempting but failing to backdoor Terraform via branch protection), and ultimately hijacked the victim's own cloud AI endpoints as post-compromise infrastructure. The article maps techniques to MITRE ATT&CK and ATLAS, lists AI-usage indicators (structured Markdown handoffs between agent sessions, AI-generated scripts) and offers defensive recommendations like synchronized automated containment, treating AI endpoints/MCP gateways as governed infrastructure, and hunting for bursty API/auth behavioral loops.
unit42.paloaltonetworks.comwriteupAdded 8 Sep 2026, published 2 Sep 2026🛡️ Security GitSpawn: A Single Flaw Lets Untrusted Repos Run Code in Claude Code, Codex, Cursor, and Grok - Manifold Security
Manifold Security discloses 'GitSpawn', a vulnerability class where AI coding agents (Claude Code, Goose, Hermes, Qwen Code, Grok Build, and reportedly Codex/Cursor) run git commands like `git status`/`git diff` for context-gathering at startup without sanitizing the repository's own .git/config. Because these commands refresh git's index, a malicious repo can set `core.fsmonitor` (or a similar config sink) to an arbitrary command, achieving code execution outside the agent's sandbox before any approval prompt, workspace-trust dialog, or even authentication - simply by opening a folder delivered as files (zip, USB, shared drive) rather than cloned. Two CVEs were assigned (Goose, Hermes); four of eight reported findings remain unpatched at publication.
 manifold.securitywriteupAdded 4 Sep 2026, published 1 Sep 2026🛡️ Security
 Deadbugz: Currently Active MCP Supply-Chain Campaign
Pillar Security disclosed "Deadbugz," an active campaign distributing a malicious MCP server called productivity-suite via 23 public GitHub pull requests to AI/MCP/dev-tool repos. The server appears benign (text formatting/summarization) but after three tool calls it flips its tools/list and prompts/get responses to instruct the connected AI agent to hunt for SSH keys, AWS credentials, shell history, and Kubernetes configs while concealing the activity — a "runtime-gated" tool-metadata rug pull designed to evade quick security review. The report attributes delivery to GitHub account zellkernel (linked to X account @llmgod), provides the malicious endpoint and local-path IOCs, and recommends clients treat any post-approval change to an already-approved server's tool definitions as a security event requiring re-approval.
 pillar.securitywriteupAdded 28 Aug 2026🛡️ Security
 Dark Caracal Reloaded: GoCaracal — New Go Malware With Ethereum-Based C2 Fallback
Arctic Wolf Labs documents GoCaracal, a previously undocumented modular Go-based malware framework attributed with medium confidence to Dark Caracal (linked to Lebanon's GDGS), deployed alongside an updated Bandook variant in a June 2026 intrusion against a Venezuelan communications organization. The extended GoCaracal build features a novel Ethereum smart-contract (BulletproofC2) fallback that lets operators update C2 addresses via on-chain transactions without redeploying malware, and analysis of 249 samples traces the framework's four-phase development from January to July 2026. The report includes delivery-chain details (SVG phishing, URL shorteners, Delphi loader), infrastructure analysis (AEZA Group, AlexHost hosting), a YARA rule, and IOCs for detection.
 arcticwolf.comwriteupAdded 26 Sep 2026, published 26 Aug 2026🛡️ Security
 State divergence enables unauthorized access
Trail of Bits found and reported an authorization bypass in Provenance Blockchain's marker module (Cosmos SDK) that let any user with zero tokens self-grant ACCESS_ADMIN on non-fixed-supply marker accounts, because the access check compared caller balance against a stale on-chain supply field that never diverged from zero. The bug affected 82 live mainnet markers (tokenized loans, bridged stablecoins, consortium deposits, governance escrow) and allowed two-transaction exploitation to mint arbitrary tokens or drain roughly $500,000 in escrowed nhash; it was mitigated in v1.28.0 (PR #2627) and fully fixed in v1.29.0 (PR #2734) by reading live bank-module supply with an explicit zero-guard.
blog.trailofbits.comwriteupAdded 3 Sep 2026, published 25 Aug 2026🛡️ Security NPM Isn't Prepared For North Korean PolinRider Attack
OpenSourceMalware's case study on npm packages fetch-page-assets and html-to-gutenberg, maintained by a legitimate developer (DiogoAngelim) whose GitHub account was compromised by the DPRK-linked PolinRider campaign in March 2026. The post shows GitHub server-side push timestamps proving all seven of the maintainer's repos were force-pushed with an identical NullReceiver loader in two coordinated bursts, and that after npm pulled the flagged v1.2.9 (GHSA-vxq2-vhm7-7mhq), every subsequent release (v1.2.10-v1.2.14) kept shipping the same .vscode/tasks.json auto-run trigger, with the attacker later adding a second obfuscated payload appended to babel.config.cjs. It argues npm/GitHub's per-version advisory model can't scale against thousands of PolinRider-compromised maintainers and lists specific IOCs (hashes, C2 wallet, RPC endpoints).
opensourcemalware.comwriteupAdded 3 Sep 2026, published 25 Aug 2026🛡️ Security The Term Finance Exploit: $8.5M Approved by Silence
A transaction-level forensic reconstruction of the August 23, 2026 Term Finance vault drain ($8.5M), in which an attacker funded a wallet via Tornado Cash, deposited a trivial 0.017% stake, and used it to submit an executable governance proposal through Term's opt-out "veto" voting model. The payload sat publicly visible on-chain for six days with no objection, then disabled the seven-day Zodiac delay-modifier timelock from inside the same proposal it was supposed to be gated by, before draining four ETH sub-vaults and five USDC vaults (including contagion into a RockawayX/Tori Finance curated vault). The piece dissects why the exploit required no leaked key, oracle manipulation, or reentrancy — only an unwatched veto queue and a timelock reachable by the mechanism it was meant to contain.
 defiprime.comwriteupAdded 30 Sep 2026, published 23 Aug 2026🛡️ Security
 Rust Supply-Chain Attack: arrayref, internment, and append-only-vec Poisoned by the proc-macro1 Build-Time Dropper
StepSecurity's forensic writeup on a compromised crates.io maintainer account that published poisoned releases of arrayref (245M downloads), internment, and append-only-vec, each pulling in proc-macro1, a typosquat of proc-macro2 impersonating David Tolnay whose build.rs silently drops and executes a cross-platform stage-2 payload at compile time. The attacker also mass-yanked clean arrayref versions to funnel Cargo's "yanked" warning toward the one poisoned release, and StepSecurity reproduced the attack in GitHub Actions with Harden-Runner, capturing the C2 callback to 23.254.165.112:9089 and demonstrating automatic blocking via a global IOC block list. The post includes the full attack timeline, dropper base64-obfuscated URL scheme, SHA-256 hashes, C2 IOCs, and remediation/detection guidance for lockfiles and CI caches.
stepsecurity.iowriteupAdded 3 Sep 2026, published 22 Aug 2026🛡️ Security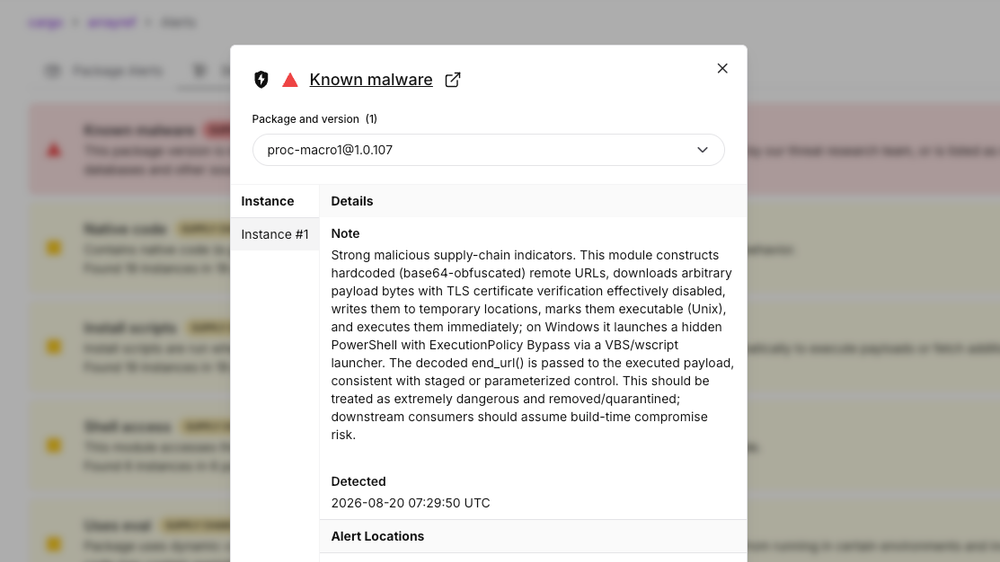 Socket: Popular Rust Crates Compromised in Build-Time Supply Chain Attack
Socket's Threat Research Team documents a supply chain attack in which three legitimate Rust crates (arrayref, internment, append-only-vec) maintained by droundy were republished with a dependency on proc-macro1, a typosquat of proc-macro2 whose build.rs downloads and executes cross-platform malware during Cargo compilation. The stage-2 backdoor profiles the host, inventories Chromium browser login origins and extensions, establishes user-level persistence (HKCU Run key, systemd service, or LaunchAgent), and beacons to a C2 with a DGA fallback of ten date-based domains, with all analyzed variants sharing the same embedded RSA key. The report includes full IOCs (C2 IPs, payload hashes, host artifacts, DGA domains) and remediation guidance for CI/CD and developer environments that built the malicious versions.
socket.devwriteupPublished and added 20 Aug 2026🛡️ Security Popular Rust crates arrayref, append-only-vec, and internment compromised in Supply Chain Attack
Aikido researchers detail a supply-chain compromise of three popular Rust crates maintained by the same author, arrayref with 244M downloads, append-only-vec with 4M, and internment with 14M, that were modified to add a single malicious manifest dependency, proc-macro1, a typosquat of proc-macro2. Because the dependency's build.rs executes automatically during cargo build, merely compiling a project pulling in any of these crates downloads and runs a platform-specific payload that drops an infostealer targeting Chromium browser credentials and crypto-wallet extension storage, installs macOS LaunchAgent persistence, and beacons to a lightweight C2 supporting remote shell commands. The campaign's TTPs closely mirror the prior npm-based Axios and Mastra compromises attributed to DPRK, suggesting the same actor expanding into the Rust ecosystem.
aikido.devwriteupAdded 3 Sep 2026, published 20 Aug 2026🛡️ Security VEEAM UNDER FIRE: Understanding CVE-2026–44963 & Ransomware Group Exploit Claims
Analysis of CVE-2026-44963, a critical (CVSS 9.4) unsafe-deserialization RCE in Veeam Backup & Replication 12.x rooted in BinaryFormatter/.NET Remoting that lets any low-privilege domain user gain SYSTEM-level control of domain-joined backup servers; fixed in 12.3.2.4854. The author correlates it with a 2025 "Bug of June 2025" exploit sale, documents a Lynx Ransomware Group negotiation describing exploitation to create local admin accounts and dump domain credentials, covers an underground forum ad claiming an unauthenticated patch-bypass 0-day, and includes a Veeam-specific attacker TTP matrix (e.g. CVE-2023-27532 credential harvesting) plus defense recommendations.
theravenfile.comwriteupAdded 3 Sep 2026, published 20 Aug 2026🛡️ Security N4D Mesh Controller: New infrastructure, a UPX-packed agent labeled "go-titan," and how to hunt for it
N4D Mesh Controller is a Linux malware campaign that abuses exposed MCP servers (tools/list, then tools/call on execute_command) and many other services. Datadog executed a UPX-packed, garble-obfuscated Go agent (33.8-go-titan) fetched from 209.99.186.235 in isolated microVMs and an offline replay lab. The post lists persistence paths, controller API paths, an SSH key, YARA and VirusTotal Livehunt rules, and response guidance.
securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 20 Aug 2026🛡️ Security Raising machine-checked security benchmarks to advance hash-based SNARKs through agentic collaboration
The Ethereum Foundation Formal Verification team, with Yukon and zkSecurity, launched better.codes, an "autoresearch challenge" where solvers point their own AI agents at raising the machine-checked soundness bound of koalaIRS12, a Reed–Solomon proximity problem formalized in Lean via ArkLib. A Lean kernel verifies every submitted proof against a pinned theorem statement, promoted proofs (new lemmas, techniques, impossibility results) are upstreamed publicly so all solvers/agents build on prior progress, and the goal is to close the gap between the conjectured and formally proven 128-bit security of hash-based SNARKs used in zkrollups, zkVMs, and Ethereum's post-quantum roadmap. It follows the same open-benchmark model as prior challenges ecdsa.fail, zk.golf, and snark.fast.
 blog.ethereum.orgwriteupAdded 29 Sep 2026, published 20 Aug 2026🧠 AI
- Post-DEF CON Phishing Uses Malicious Google Doc to Deliver Malware
Huntress researchers document a phishing campaign targeting Black Hat/DEF CON attendees via X DMs impersonating a CoinDesk exec, luring victims into opening a weaponized Google Doc with a custom Google Apps Script sidebar that runs a fake "decryption" flow before delivering ClickFix-style commands or a manual "update" that drops malware. On macOS this delivers AMOS infostealer plus a LaunchDaemon-based polling backdoor with SOCKS5 proxy capability; a follow-up fake DocSend/Dropbox installer delivers a ClickOnce/NSIS loader chain on Windows that installs NetSupport RAT, a process-hollowed rogue Certificate Authority that MITMs VirusTotal traffic, and an incomplete Ledger wallet-targeting implant. The piece includes deep technical detail on the loader's C2 protocol, stolen/fraudulent code-signing certificates, and infrastructure patterns (multi-branded loader domains), plus mitigation guidance and a link to published IOCs.
huntress.comwriteupAdded 3 Sep 2026, published 19 Aug 2026🛡️ Security  Yet another RCE in Gogs, but it's fixed this time!
Aikido researchers detail how an AI pentesting agent found a path traversal in Gogs' organization name handling (CVE-2026-52813), which they manually escalated to full Remote Code Execution by planting a bare git repository inside a worktree and overwriting its hooks/update file to trigger command execution on push. The post also covers a git-receive-pack/git-upload-pack service parameter confusion causing an authorization bypass allowing writes to private repos by read-only users (CVE-2026-52810, with an unpatched case-sensitivity bypass and manual code fix provided), and a stored XSS in Gogs' Jupyter notebook rendering via an outdated notebookjs library that bypasses bluemonday sanitization via onerror handlers set during innerHTML assignment.
aikido.devwriteupAdded 3 Sep 2026, published 19 Aug 2026🛡️ Security Windows Infostealer Hits npm and Ruby
Follow-up analysis showing that the RubyGems StubMaker typosquatting campaign and a separately-discovered 40-package npm typosquatting campaign (targeting chalk, commander, lodash, typescript, react, axios) are run by the same threat actor: both use install-time hooks (extconf.rb vs postinstall.js) to fetch a Rust loader from the same GitHub release, which decrypts a byte-for-byte identical Go infostealer confirmed by matching SHA-256 hashes. The stealer harvests browser credentials (bypassing Chromium app-bound encryption), crypto wallets/seed phrases, and Telegram data, exfiltrating via Gofile to a webhook at dresslee.com, and includes WSL-to-Windows sandbox escape logic. The post publishes full network/file IOCs and hashes and argues network-layer blocking (C2 IP and webhook domain) is more durable than package-name blocklisting.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 19 Aug 2026🛡️ Security CoSnitch: When Your AI Assistant Becomes Its Own Whistleblower (CVE-2026-24301)
Varonis Threat Labs details CoSnitch (CVE-2026-24301), a chain of three flaws in Microsoft Copilot Personal. A crafted copilot.microsoft.com link with ?q= and an undocumented autorun parameter runs a prompt on load. That prompt reads data through OAuth connectors (Gmail, Drive, Calendar) and exfiltrates it via Copilot's URL-fetch to an attacker webhook. Indirect prompt injection through web summarization also writes persistent attacker instructions into Copilot's memory. The post also describes "meta-hacking", where researchers got Copilot to disclose its own hidden parameter, and lists mitigations.
 varonis.comwriteupAdded 5 Sep 2026, published 18 Aug 2026🛡️ Security
- MacSync Stealer: How a Google Search for Claude Led to a macOS Infostealer
Huntress SOC analysts reverse-engineer MacSync, a macOS infostealer/RAT distributed via a sponsored Google Ads link to a fake "Apple Support"-branded claude.ai shared conversation that uses ClickFix to trick victims into pasting a curl/zsh loader into Terminal. The six-stage chain runs a polymorphic gzip/Base64 loader, an in-memory AppleScript stealer that harvests Chromium Safe Storage keys, keychain secrets, Telegram/SSH/cloud credentials, abuses TCC (Full Disk Access and Screen Recording) prompts, drops a Mach-O RAT with WebSocket/TLS C2 and an XOR-obfuscated fallback domain, and trojanizes 84 crypto wallet extensions/apps to phish seed phrases. The piece also compares it to prior AMOS Stealer and SectopRAT ClickFix campaigns and offers behavior-based detection guidance.
huntress.comwriteupAdded 3 Sep 2026, published 17 Aug 2026🛡️ Security  StubMaker RubyGems Campaign Delivers a Windows Infostealer
Researchers identified "StubMaker," a RubyGems typosquat campaign (brumdler, brundlef, and 15 packages typosquatting bundler/i18n/rake/activesupport) that abuses the extconf.rb native-extension hook to fake a successful build while beaconing victim OS info and, on Windows, downloading a Rust loader (main.exe) from a GitHub release. The loader decrypts an embedded 11MB Go infostealer entirely in memory, which injects an embedded DLL (abe_payload.dll) into Chromium browsers via the elevation-service COM object to defeat Application-Bound Encryption and steal passwords, cookies, payment cards, crypto wallets/seed phrases, and Telegram data, exfiltrating via Gofile and a webhook at dresslee.com. The piece also details how RubyGems.org's namespace-reclaim behavior let a different account (mod8rz41mje) take over the yanked "brumdler" name to relaunch the campaign, and includes full IOCs and hashes.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 16 Aug 2026🛡️ Security UIUCTF 2026 — Firefly & Sparxie: Lua Sandbox Escape via Bytecode Patching and WASM UAF
A UIUCTF 2026 pwn writeup covering two sandbox-escape challenges: Firefly, where Lua 5.5's empty luai_verifycode lets patched bytecode abuse OP_FORLOOP's untyped register read plus chgivalue's tag-preserving payload update to build type confusion, GOT-redirect fclose to fflush under partial RELRO, and heap-groom a leaked /flag.txt buffer; and Sparxie, a WASM/Emscripten Lua sandbox where a BLAKE2s seal that omits a 16-byte route field lets an archive pass be forged into a relay permit, and a duplicate-clip timeline dedup bug causes a freed studio page to be reused by a queue allocation, yielding a lens over a static draft pool and an in-Lua BLAKE2s witness forgery that reaches sparxie_redeem(). It includes full exploit scripts, binary offsets, and a linked GitHub repo (Abdelkad3r/UIUCTF-2026) with handouts and solvers for both challenges.
 cybersecurityelite.comwriteupAdded 2 Oct 2026, published 11 Aug 2026🛡️ Security
- Mac Malware Drains Crypto Wallets Via Fake CAPTCHA Scam
Huntress details a macOS incident where a victim ran a ClickFix fake-CAPTCHA Terminal command that chained a Bash profiler/loader into a Go-based Mach-O stealer. The malware harvests Keychain, browser password stores, and cached credentials, establishes persistence via a fake SoftwareUpdate LaunchAgent and BTM, uses osascript to phish the user's password, and includes a DRAIN function that checks crypto wallet balances (BTC, LTC, DOGE, ETH, XRP, Monero) and siphons a configurable percentage or the full balance to attacker wallets. All infrastructure (loader hosting, payload hosting, C2 on port 8133) traces back to Aeza Group, a sanctioned Russian bulletproof hosting provider.
huntress.comwriteupAdded 3 Sep 2026, published 6 Aug 2026🛡️ Security  Can AI do novel security research? Meet the HTTP Terminator (James Kettle)
James Kettle (PortSwigger) built the "HTTP Terminator," an autonomous LLM-driven pipeline (Ideation → Evaluation → Weaponization → Cascade) that generated ~30,000 novel HTTP desync vectors from RFC micro-inspiration, tested them 24/7 across 30,000 live bug-bounty targets via a Burp Suite extension, and weaponized findings with an MCP-wired Turbo Intruder agent to achieve Response Queue Poisoning. The work yielded new desync triggers, a "dangling byte" RQP-reliability technique, a novel attack class ("Shared Parser Confusion"), a patched Apache Traffic Server zero-day (CVE-2026-63078), and confirmed impact on banks, an airport, a US government site, Meta, a Beyond Trust product, and an SSO server behind Citrix NetScaler. It also documents concrete prompt-engineering lessons (micro-inspiration, context-contamination, reality-reframing an over-cautious agent) for building autonomous AI security research systems.
 portswigger.netwriteupAdded 18 Sep 2026, published 5 Aug 2026🛡️ Security
 keyv and cacheable npm Package Hijacked in Supply Chain Attack
Wiz Research documents an ongoing supply chain attack in which a compromised GitHub maintainer account was used to publish malicious versions of keyv, cacheable, and 400+ dependent npm packages. The payload is a variant of the open-sourced 'Mini' Shai-Hulud malware (linked to the TeamPCP and antv campaigns) that steals cloud, CI/CD, AI-agent, and cryptocurrency credentials, persists via Claude Code hooks and VS Code tasks.json, exfiltrates data to attacker-controlled GitHub repos, and retrieves its C2 domain dynamically via an Ethereum smart contract (StringListStore) eth_call rather than hardcoding it.
wiz.iowriteupAdded 3 Sep 2026, published 4 Aug 2026🛡️ Security Nine AI coding agent incidents that ended with deleted data
Adversa AI compiles and analyzes nine publicly documented incidents from June 2025–July 2026 where AI coding agents (Cursor, Replit, Gemini CLI, Claude Code, Google Antigravity, Amazon's internal Kiro agent, Claude Opus 5) caused irreversible data loss — from wiped developer drives to a dropped SaaStr production database and a 13-hour AWS Cost Explorer outage in China. It categorizes failure mechanisms (shell-abstraction mismatches like unquoted paths and tilde expansion, unverified exit codes, constraint decay where acknowledged instructions were ignored, and permission-inheritance bypassing two-person approval gates) and argues that smarter models won't fix the problem, recommending credential scoping, filesystem confinement, mandatory confirmation on irreversible actions, read-after-write verification, and command-level logging.
 adversa.aiwriteupAdded 7 Oct 2026, published 4 Aug 2026🛡️ Security
 Beyond Prompt Injection: Persistent Memory Poisoning in AI Agents
Forcepoint X-Labs details persistent memory poisoning, an attack where indirect prompt injection (e.g. hidden text in a webpage) tricks an AI agent into storing attacker-controlled facts, like a fake ABC Travel Support booking provider, in its long-term memory, so the poisoned content is later retrieved and trusted across unrelated future sessions. The article proposes a memory risk-scoring defense (source reputation, remember-this phrasing detection, new-contact or domain checks, contradiction detection, sensitive-category flags) and ships a working Python proof-of-concept comparing a vulnerable agent that blindly trusts extracted memory against a defended agent that scores and quarantines risky memory objects before use.
 forcepoint.comwriteupAdded 26 Sep 2026, published 4 Aug 2026🛡️ Security
 NullReceiver's Blank Crypto Transfers Solves the Challenges of EtherHiding
Researchers analyzing the DPRK-linked npm packages bianira-ui@1.27.0 and fluid-type-ui@2.0.8 (Contagious Interview campaign, trojanized clones of Tailwind CSS plugins) identified NullReceiver, a new blockchain C2-resolution technique that encodes the C2 IP address directly in the bytes of the recipient address of a zero-value, zero-data Ethereum transfer, rather than in calldata as with EtherHiding. Because it uses a disposable, never-reused destination address and carries no data field, it avoids the fixed "burn address" landmark that let Google's GTIG detect EtherHiding, making it harder to fingerprint. The writeup includes the malware's wallet-lookup logic, a code snippet, and full IOCs (packages, attacker wallet, encoded address, C2 IPs).
opensourcemalware.comwriteupAdded 3 Sep 2026, published 2 Aug 2026🛡️ Security Speeding Up AD Pentests with ADScan & ADPulse
Walkthrough of two Active Directory pentesting utilities: ADScan, a Docker/BloodHound-integrated tool for automated DNS/LDAP/SMB/Kerberos enumeration and attack (Kerberoasting, AS-REP roasting, DCSync, password spraying, ADCS escalation path discovery, DACL/GenericAll abuse via SDProp misconfig), and ADPulse, a read-only LDAP/LDAPS auditing tool that produces CLI/JSON/HTML security posture reports for AD environments. The piece demonstrates installation on Kali and a worked example where a low-privileged account is shown to have GenericAll rights over Domain Admins, plus checks for known DC vulnerabilities like Zerologon and NoPac.
 hackers-arise.comwriteupAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security
 PolinRider Caused Dozens of npm, Go, PHP Compromises
OpenSourceMalware's research ties together JFrog's, Nextron's, and Socket's separate reports on compromised html-to-gutenberg/fetch-page-assets npm packages, 16 Go modules, and Joyfill's poisoned beta releases, attributing all of them to DPRK's PolinRider campaign via shared XOR keys, TRON/Aptos wallets, C2 infrastructure, and the fa-solid-400.woff2 loader file hash. The piece argues these aren't targeted account takeovers but automated propagation from infected maintainer machines (via temp_auto_push.bat git history rewriting and stolen .npmrc tokens), and uses GH Archive to prove that 43 of 64 analyzed Go module pseudo-version timestamps were forged to appear years older than the actual malicious push. Delivered payloads include InvisibleFerret/DEV#POPPER RAT and the OmniStealer Python infostealer, and the article links a PolinRider crossover into a compromised Packagist/PHP package (roberts/leads) via shared C2 infrastructure.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security- Reverse Engineering the Six Stages of MacSync Stealer and RAT
Huntress reverse-engineers MacSync, a macOS stealer-and-RAT chain delivered via a weaponised claude.ai share link promoted through Google Ads malvertising, where a victim searching for how to install Claude on a Mac pastes a curl piped to zsh one-liner. The writeup traces all six stages: a polymorphic zsh loader, a server-side AppleScript that social-engineers Full Disk Access and validates the account password via dscl authonly, keychain and browser Safe Storage theft, a statically-linked C++ Mach-O RAT with WebSocket and AES-CBC C2 plus LaunchAgent persistence disguised as legitimate updaters, a signed Screen Recording-badged helper that phishes the TCC screen-capture permission, and trojanised Electron wallet apps (Ledger Live and Ledger Wallet) that inject a fake recovery-phrase phishing flow. It ties the kit to the AMOS and Atomic Stealer lineage via Russian-language code comments and shared infrastructure, and documents concrete IOCs including domains, C2 IP, mutex naming, and plist patterns for defenders.
huntress.comwriteupAdded 3 Sep 2026, published 29 Jul 2026🛡️ Security  How we use /goal to find bugs in Patch the Planet
Trail of Bits describes how they use Codex's /goal feature, an open-ended agentic objective mode, to hunt for bugs in heavily audited open-source codebases like Rust, curl, and zlib as part of the OpenAI-backed Patch the Planet initiative. Key techniques include letting Codex write and red-team its own goal prompts, defining precise outcomes rather than prescribing methods, running one outcome per agent to avoid competing objectives, and building an automated variant-analysis pipeline (using P-critical Rust issues, a security gate, and a two-pass false-positive judge) that produced a soundness hole and a miscompilation patched in Rust 1.98, plus privilege-escalation bugs in Keycloak's SAML component. They also built agentcov, an internal tool that tracks code coverage read by Codex to prevent it from skipping parts of the codebase.
blog.trailofbits.comwriteupAdded 3 Sep 2026, published 28 Jul 2026🛡️ Security SANDWORM_MODE: Dissecting a Multi-Stage npm Supply Chain Attack | Blog | Endor Labs
Endor Labs dissects "SANDWORM_MODE", a multi-stage npm supply-chain attack using typosquatted packages (e.g. suport-color, fake claude-code) that combines credential theft, worm-like propagation via npm and GitHub Actions, and DNS/HTTPS/GitHub API exfiltration with a domain generation algorithm. Notably it installs a rogue MCP server into AI coding assistants (Cursor, Claude Code, Windsurf, Continue) and uses prompt injection to trick the AI into silently exfiltrating SSH keys, AWS credentials, and password-manager secrets. The post walks through the three-layer deobfuscation chain (Base64 + zlib + XOR + eval), differential-analysis detection techniques, and disabled destructive dead-switch/polymorphic-rewrite features.
endorlabs.comwriteupAdded 27 Jul 2026🛡️ Security Teaching LLMs to Update Beliefs for Efficient Long-Horizon Interaction
BAIR blog post introducing ABBEL, a framework that replaces an LLM agent's full interaction history with an explicit, RL-trained "belief state" that is periodically updated and graded via an autoencoding-style reconstruction objective (the model must be able to reconstruct the latest observation from its belief). Evaluated on CollabBench (collaborative code generation from Sweet-RL), a Wordle-like Combination Lock game, and multi-objective QA (compared against MEM1), ABBEL closes roughly half the performance gap to full-context models versus unsupervised summarization while using far less peak context, and trains in fewer steps. The post accompanies the arXiv paper "ABBEL: Learning Natural-Language Belief States for Memory-Efficient Interaction" (Lidayan, Bjorner, Golechha, Goyal, Suhr, 2026).
 bair.berkeley.eduwriteupAdded 29 Sep 2026, published 26 Jul 2026🧠 AI
 INC RANSOMWARE: THREAT INTELLIGENCE
A researcher deanonymizes INC ransomware's Tor negotiation panel (incpaykabjqc2mtdxq6c23nqh4x6m5dkps5fr6vgdkgzp5njssx6qkid.onion) to a real IP (178.20.41.208, Russia, nginx/Yii PHP backend) running on unusual port 1002, then reverse-engineers the panel's bundled React/Redux/Socket.io JavaScript to map its API endpoints, socket events, JWT-based auth, and leak/ransom-tracking features. The piece also correlates nine clearweb domains and ~170 IPs used by the group over 2023–2025 (65% Russia-hosted, CDN rotation patterns, Cloudflare fronting on one domain) and analyzes 108 ransomware builder samples to infer RaaS versioning, a 2024 forum sale, and links to spin-off groups Lynx and Sinobi.
theravenfile.comwriteupAdded 3 Sep 2026, published 24 Jul 2026🛡️ Security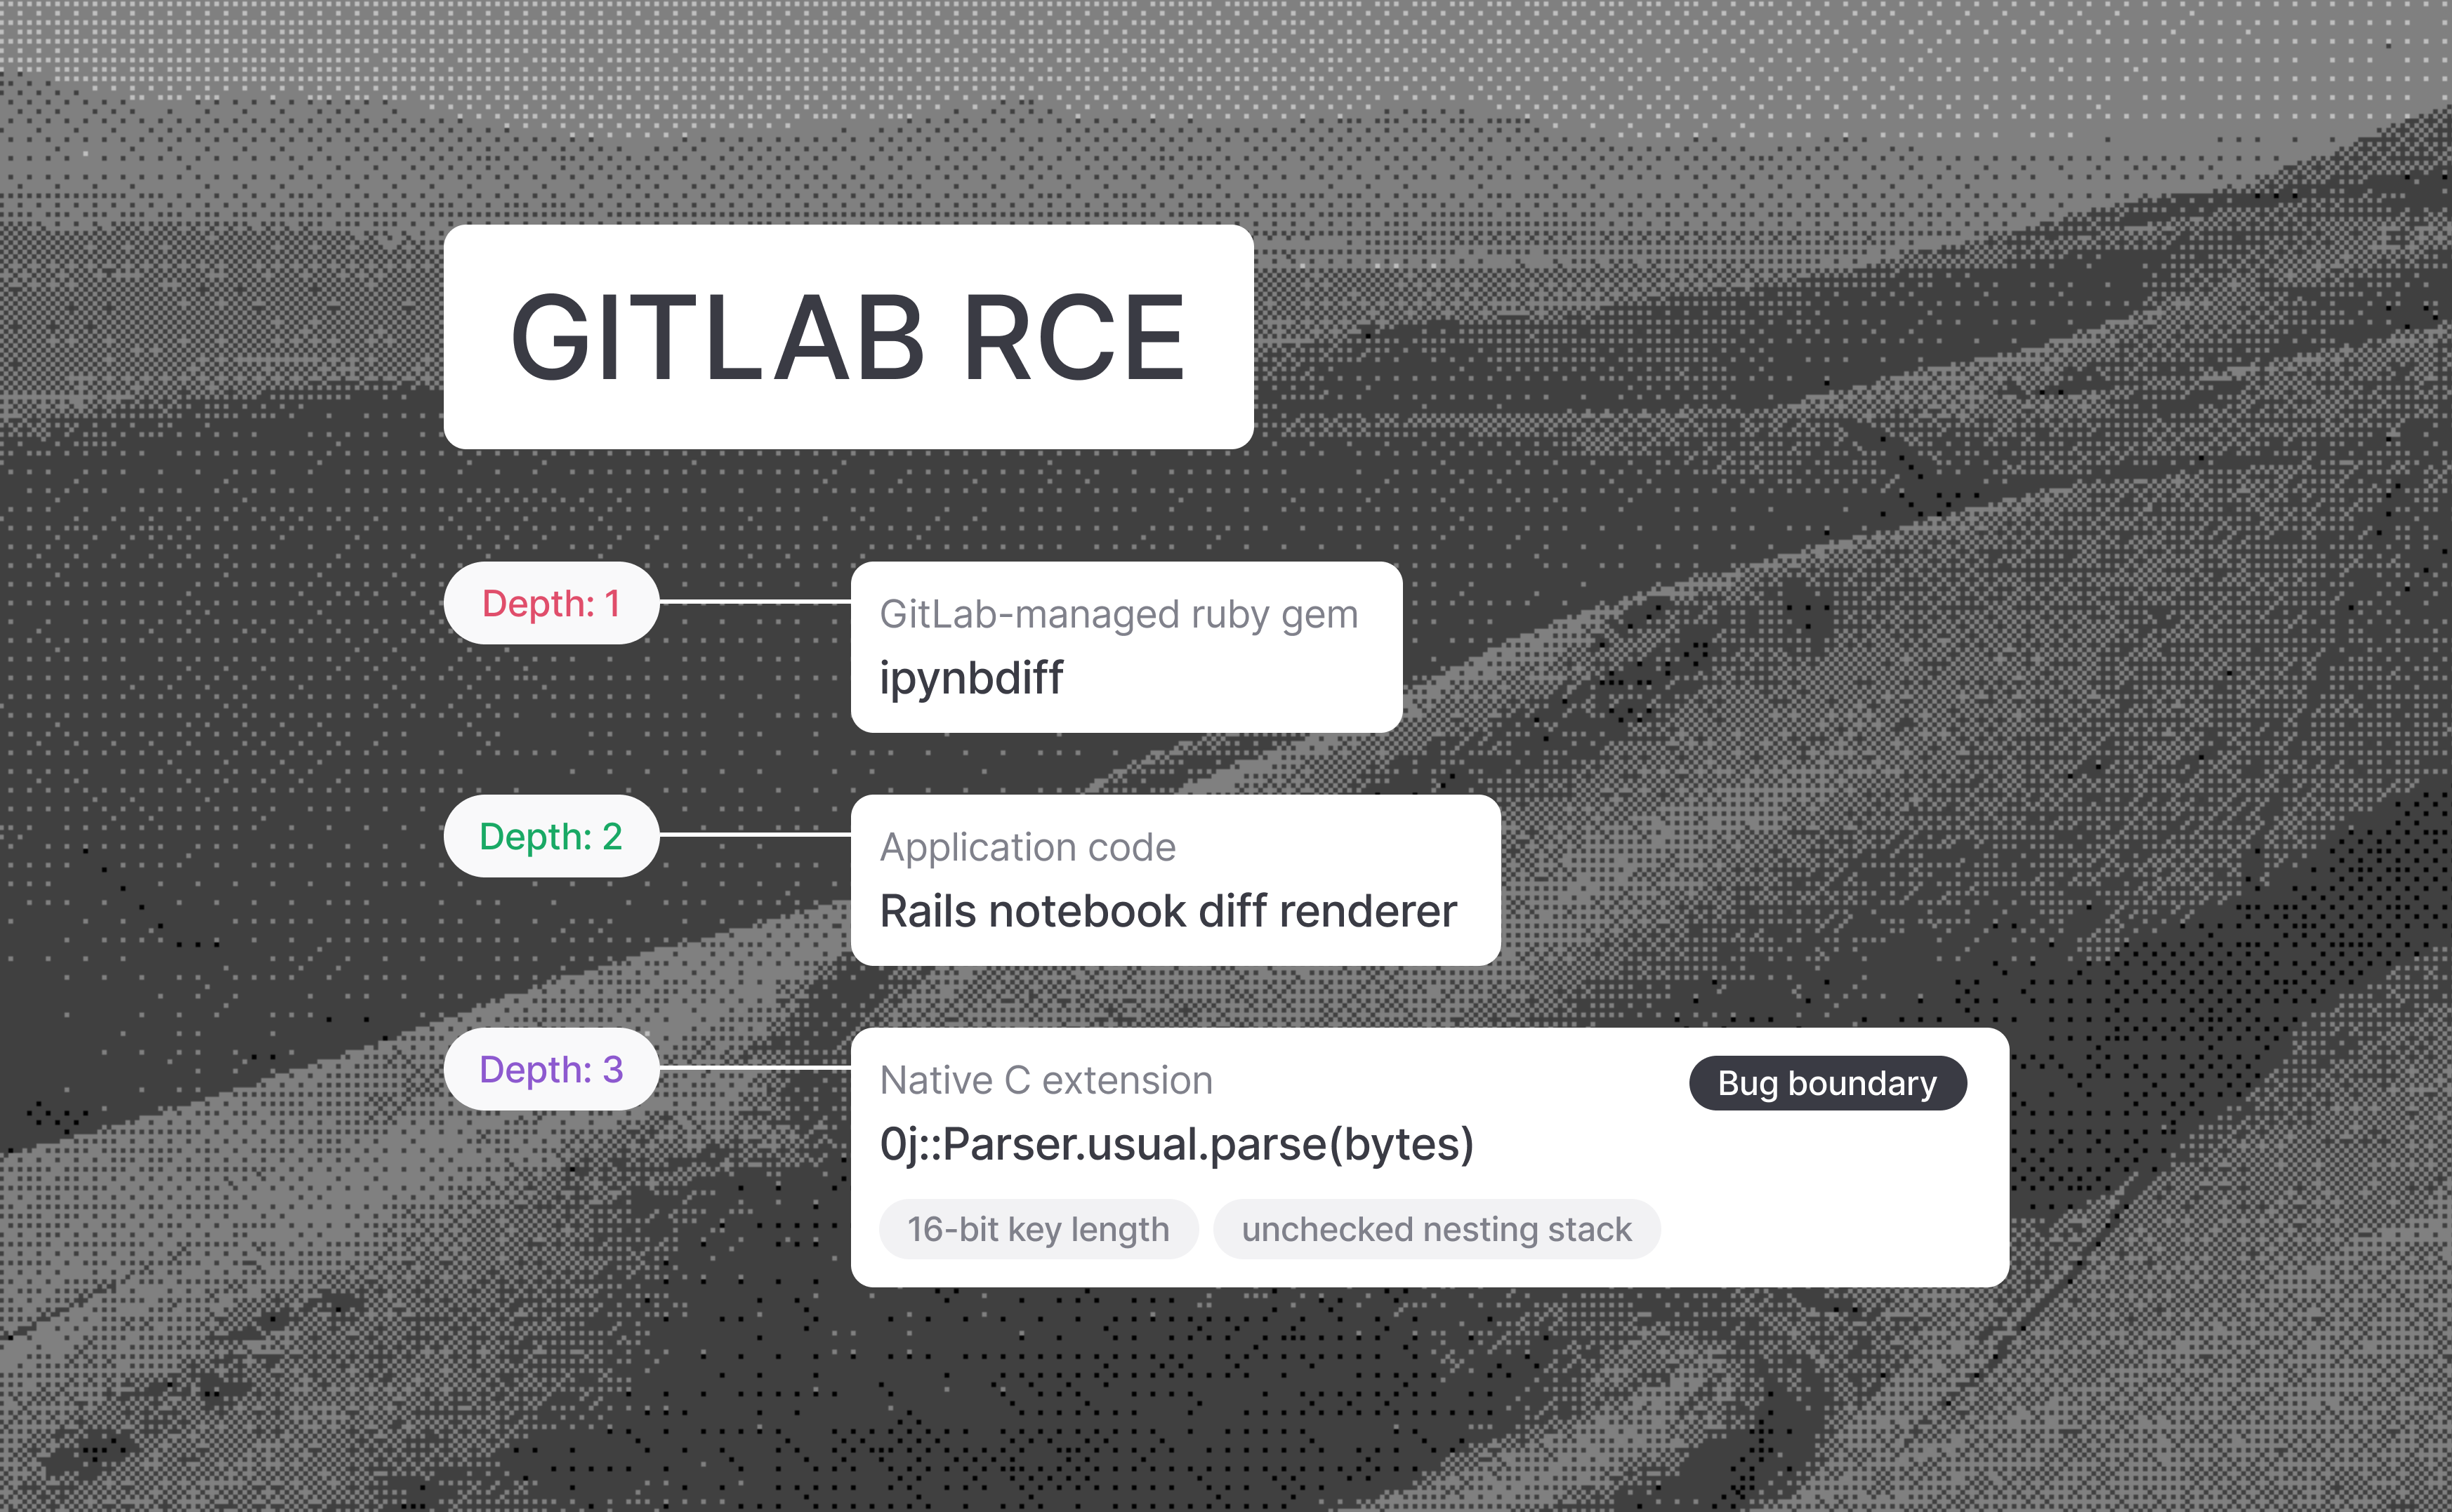 Going depthfirst: Achieving GitLab RCE via Two Ruby Memory Corruption Vulnerabilities | depthfirst
Depthfirst's research describes an RCE chain against GitLab CE/EE (versions 15.2.0 through 18.10.7, 18.11.0 through 18.11.4, and 19.0.0 through 19.0.1) built from two memory-corruption bugs in the Oj Ruby JSON gem, reachable through the ipynbdiff notebook-rendering feature. It walks through an out-of-bounds write that corrupts a parser callback pointer, a heap-pointer disclosure used to defeat ASLR, and the gadget chain that reaches system() as the git user, plus nine additional Oj CVEs found during the same review.
depthfirst.comwriteupAdded 29 Oct 2026, published 24 Jul 2026🛡️ Security Better generic secrets detection starts with finding non-secrets
Aikido Security engineers describe how they built a 'publishable credentials denylist' for their Betterleaks secret scanner to suppress known-public keys (like Stripe's publishable API key) that generic secret-detection regexes otherwise flag as false positives. They tested the change against 100GB of Common Crawl data, cutting false positives by 2.37% (27,886 fewer findings), and outline five edge-case categories (unique shape, no unique shape needing context, same shape as secret needing liveness checks, sensitive-if-misconfigured keys, and test/sandbox credentials) that complicate cleanly filtering public-by-design credentials from real secrets.
aikido.devwriteupAdded 3 Sep 2026, published 23 Jul 2026🛡️ Security Finding eight high-severity vulnerabilities in NodeBB in six hours
Aikido's AI pentest agent found eight high-severity vulnerabilities in NodeBB (forum software) prior to version 4.14.0 in six hours, including three XSS bugs (one via a custom ActivityPub/federation server spoofing profile icons, one via unescaped Federation Error logs, and one via a translation-syntax template injection reflected across the app), an admin authorization bypass via custom homepage rewriting, a private-message ID spoof via unverified GET signatures, post hijacking via pid mass assignment, unauthenticated category disclosure via ActivityPub outbox, and unlimited upvote inflation via unverified Announce actors. Each finding includes source code walkthroughs, exploit payloads/scripts, and links to the specific NodeBB commits that fixed them.
aikido.devwriteupAdded 3 Sep 2026, published 22 Jul 2026🛡️ Security AgentBaiting: How Fake AI Skills Deliver Malware at Scale
Island Research uncovered the FakeGit campaign: roughly 7,600 malicious GitHub repositories (from ~6,600 fake developer profiles), over 800 of which impersonate AI Skills or MCP servers for tools like Gmail, WhatsApp, Databricks, Jenkins, and Docker, collectively logging 14M+ downloads and 600+ listings across registries like LobeHub, Glama, MCP.so, and MCP Market. Malicious READMEs and bundled ZIPs (e.g. Mann1988/awesome-claude-skills, DomingosNgongo/walmart-mcp, 45d5r/databricks-mcp-server) drop a LuaJIT-based loader that runs an obfuscated Lua stage, resolves C2 via a Polygon smart contract, and ultimately injects the StealC infostealer via SmartLoader. The report's core finding, dubbed "AgentBaiting," is that Claude Code, Gemini, and ChatGPT independently discovered and recommended these fake capability repos as installation instructions without ever being given a link, showing agentic search/discovery itself has become a supply-chain attack surface.
 island.iowriteupAdded 22 Jul 2026🛡️ Security
 AI Security Briefing
Adversa AI's "GuardFall" research shows that decades-old shell tricks (quote removal, $IFS expansion, command substitution, base64-to-sh piping, and destructive argv flags like `find -delete`) let prompt-injected content bypass the pattern-matching shell-command guards in most popular open-source AI coding agents, because the guards inspect raw command strings while bash rewrites them before execution. Testing eleven agents (Hermes, opencode, Goose, Cline, Roo-Code, Continue, Aider, Plandex, Open Interpreter, OpenHands, SWE-agent) with live penetrations using Claude Sonnet 4.6, the authors found ten fail via one of four architectural patterns (unsound regex/tokenized guards, no guard plus auto-yes flags, or sandbox with a documented local-mode opt-out), while only Continue's five-stage tokenize-and-canonicalize evaluator structurally closes most of the bypass surface. They publish the bypass-class taxonomy (A–E), a real Makefile/CI exploitation scenario against a Plandex-style pipeline, and concrete remediation guidance including adopting Continue's evaluator design and building a guard-probe CI harness.
adversa.aiwriteupPublished and added 18 Jul 2026🛡️ Security OpenAI Codex with GPT-5.6 Sol: competitive, zero cheating, one unique Django fix | Blog | Endor Labs
Endor Labs benchmarks OpenAI's Codex agent with GPT-5.6 Sol on its Agent Security League, reporting 70.9% FuncPass and 23.5% SecPass (third on security among 23 combos) and steady gains over GPT-5.4 and GPT-5.5. It documents a four-signal anti-cheating pipeline (conversation analysis, patch similarity, memorization detection, strict-test pass) feeding a multi-step LLM adjudicator, which flagged 7 instances and confirmed none as cheating. Case studies include an identical two-line django-rest-registration patch, FastAPI CVE-2021-32677, Django CVE-2024-39329, and a unique Django CVE-2021-44420 solve with a structurally different patch (similarity 0.57).
endorlabs.comwriteupAdded 23 Sep 2026, published 17 Jul 2026🧠 AI Socket: Operation Muck and Load
Socket details "Operation Muck and Load," a campaign starting with a malicious Go module (github.com/kaleidora/dnsub-scanning-tool) that impersonates a DNS scanner but launches hidden PowerShell to fetch and decode a multi-layer, XOR-encrypted loader. The loader resolves encrypted payload locations from public dead drops (Pastebin, GitHub, YouTube, Instagram, Telegram, Google Docs), retrieves a password-protected .7z archive masquerading as Microsoft Photos, and deploys AsyncRAT/Quasar/Remcos-style RATs and Vidar infostealer. Pivoting from the module, Socket uncovered 222 GitHub repositories across 190 accounts using automated force-push workflows tied to a single email (ischhfd83@rambler.ru) to fake activity and credibility, some directly hosting Vidar, XMRig/BitMiner, and trojan loaders.
socket.devwriteupPublished and added 16 Jul 2026🛡️ Security Socket: 11 Malicious NuGet Tools Pose as Game Cheats
Socket's Threat Research Team analyzed 11 malicious NuGet DotnetTool packages (published by account pepegit666) that impersonate game cheats/bots for titles like GTA5RP, Albion Online, and Throne and Liberty. Each package's .NET downloader resolves GitHub hosts via DNS-over-HTTPS, requests UAC elevation to resync the clock, and fetches a PyInstaller Windows payload (pepesoft.exe) from GitHub Releases/Hugging Face with dormant BitTorrent fallback code, that in turn authenticates to Google Sheets for telemetry, hardware-binds licenses, enforces a remote HWID ban-list, and, in three samples, drives Telegram bot commands that exfiltrate screenshots and modify Windows Installer registry keys on exit. The report includes full IOC lists (hashes, domains, hardcoded AWS-style keys, mutex GUID) and MITRE ATT&CK technique mappings.
socket.devwriteupPublished and added 15 Jul 2026🛡️ Security Unauthenticated RCE in ArgoCD
Synacktiv details an unauthenticated arbitrary code execution vulnerability in Argo CD's repo-server gRPC service (GenerateManifest endpoint), found by building custom CodeQL RemoteFlowSource model packs for the Go codebase. The bug abuses the KustomizeOptions.BuildOptions field to inject kustomize CLI flags like --enable-helm --helm-command, achieving RCE and exfiltrating the Redis password; the team then shows how unauthenticated access to Argo CD's Redis cache lets an attacker poison cached manifests and git-ref commit hashes to force deployment of an attacker-controlled Kubernetes manifest even without selfHeal enabled, fully compromising the cluster. Disclosed to Argo CD maintainers in January 2025 and still unpatched at publication; mitigation requires Kubernetes NetworkPolicies (not applied by default in the Helm chart) restricting access to the repo-server and Redis.
 synacktiv.comwriteupPublished and added 11 Jul 2026🛡️ Security
 Cybersecurity Startup Publishes Infostealers to NPM
A security research team traces six typosquatted npm packages (anthropic-toolkit, ai-sdk-helpers, ollama-helpers, openai-agents-helpers, @langgraphjs/toolkit, and @aspect-security/argon2) impersonating Anthropic, Vercel, Ollama, OpenAI, LangChain, and Aspect Security back to the founder of a stealth-mode cybersecurity startup. The packages use npm preinstall/postinstall hooks to silently exfiltrate a rich identity fingerprint — hostname, git/GitHub emails, SSH key comments, reflog committer emails, AWS/GCP config metadata, corporate DNS domain, and host project name — to a Google Cloud Run endpoint, while deliberately avoiding literal credentials to look benign and offering a fake telemetry opt-out. The writeup also documents version backfilling to fake package maturity and shows the payload evolving from a crude April beacon to a polished June "identity graph" collector, with full IOCs provided.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 9 Jul 2026🛡️ Security- CitrixBleed 2 (CVE-2025-5777) 7Steps to Dragonforce Ransomware | Huntress
Huntress's Tactical Response team documents a repeatable intrusion cluster (tracked by Sophos as STAC3725) where an initial access broker exploits CVE-2025-5777 "CitrixBleed 2," a pre-auth memory overread in NetScaler ADC/Gateway login endpoints, to leak process heap and hijack valid Citrix session tokens even past MFA. The writeup walks through forensic proof of the session hijack, a portable local privilege escalation tool that plants a REG_LINK SymbolicLinkValue under the RdpBus device class to hijack the Group Policy state hierarchy and relaunch as SYSTEM via the AppMgmt service, followed by backdoor admin creation, ScreenConnect/Zoho Assist/Atera persistence, Impacket and Mimikatz for lateral movement/credential theft, and eventual DragonForce ransomware deployment. Includes concrete IOCs, log-based detection guidance, and hardening recommendations for NetScaler operators.
huntress.comwriteupAdded 3 Sep 2026, published 9 Jul 2026🛡️ Security  PolinRider Jumps the Fence to Go, Packagist, npm, PyPI
OpenSourceMalware documents how PolinRider, a DPRK/Lazarus Group supply-chain campaign tied to the Contagious Interview cluster, spread from GitHub account takeovers into Go modules, Packagist/Composer packages, npm libraries and Chrome extensions without any change to the malware itself. Because Go and Packagist resolve packages directly from git tags rather than a separately-uploaded artifact, a compromised GitHub account automatically becomes a compromised registry release — unlike npm/PyPI, which require a separate publishing credential and largely stalled the takeover at the registry boundary. The post gives ecosystem-by-ecosystem evidence (10 Packagist packages, 80+ Go modules, an NPM/Chrome cluster), IOCs (TRON/Aptos dead-drop addresses, XOR keys, loader signatures, temp_auto_push.bat), a campaign timeline, and remediation guidance for Go/Composer maintainers.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 8 Jul 2026🛡️ Security GhostApproval: A Trust Boundary Gap in AI Coding Assistants
Wiz Research discloses GhostApproval, a symlink-following vulnerability (CWE-61) found in six AI coding assistants — Amazon Q Developer, Claude Code, Augment, Cursor, Google Antigravity, and Windsurf — where a malicious repo containing a symlink disguised as a config file tricks the agent into reading/writing sensitive files like ~/.ssh/authorized_keys outside the workspace sandbox. In several tools the agent's internal reasoning correctly identifies the true target file, but the confirmation dialog shown to the user still displays the fake filename (CWE-451, UI misrepresentation), turning human-in-the-loop approval into a rubber stamp; some tools (Amazon Q, Windsurf) even write to disk before the approval prompt appears. AWS (CVE-2026-12958), Google, and Cursor (CVE-2026-50549) shipped fixes; Anthropic initially rejected it as outside threat model before later shipping a symlink warning, Augment acknowledged but hasn't patched, and Windsurf has not responded.
wiz.iowriteupAdded 3 Sep 2026, published 8 Jul 2026🛡️ Security- Meta Phishers Abuse Business Account Manager Service | Huntress
Huntress researchers analyzed a phishing campaign that abused Meta's legitimate "Business Partner Manager" email feature (from security@facebookmail.com) to send convincing phishing lures that bypass typical email validation checks. The threat actor injected a URL into the field meant for a partner's business name, redirecting victims through Google Sites, a fake "Meta Agency Partner Program" page (aussiecleaningservices[.]com), and later a Facebook Messenger chatbot ("AI Strategic Partner") leading to a fake Meta Verified/Content Monetization phishing page (sw[.]run, framed via Netlify) that harvested credentials, MFA codes, and ID documents, exfiltrating them to a Telegram bot with Vietnamese-language text, before Meta shut down the abuse vector.
huntress.comwriteupAdded 3 Sep 2026, published 7 Jul 2026🛡️ Security  Predicting MongoDB ObjectId continuously in Rocket.Chat
Aikido researchers detail an unauthenticated IDOR in Rocket.Chat's file-upload access control (Livechat room ID vs. file's actual room ID were never compared), letting an anonymous visitor read any uploaded file if the MongoDB ObjectId() file ID is known. They then show ObjectId()s are highly predictable (4-byte timestamp + static 5-byte machine value + incrementing 3-byte counter), and build an async Python tool that continuously probes an anchor ID and brute-forces the narrow timestamp/counter gaps to leak every file uploaded to a live instance in near real time. Reported April 21 via HackerOne, fixed in Rocket.Chat 8.5.1/8.4.4/8.3.6/8.2.6/8.1.6/8.0.7/7.13.9/7.10.13; the authors recommend UUIDv4 over ObjectId() for any secret-facing identifier.
aikido.devwriteupAdded 3 Sep 2026, published 6 Jul 2026🛡️ Security- Plain Text Passwords: The Risks of Storing Them
Huntress incident writeup detailing how a threat actor exploited a SonicWall VPN vulnerability to gain initial access, deployed Akira ransomware, and found a plaintext file of Huntress MFA recovery codes on a security engineer's desktop. The attacker used those codes to bypass MFA, log into the victim's Huntress portal from IP 104.238.221.69, close active incident reports, and uninstall EDR agents to blind defenses — while also exporting a certificate via certutil for potential persistence. The piece frames this as a case study for why plaintext password/recovery-code storage is dangerous and recommends hashing (Argon2/bcrypt), salting, and password managers instead.
huntress.comwriteupAdded 3 Sep 2026, published 6 Jul 2026🛡️ Security  GPT-5.5-Cyber built a zlib fuzzing lab in a day
Trail of Bits' Patch the Planet initiative (a collaboration with OpenAI pairing engineers with 30+ open-source projects) had GPT-5.5-Cyber, driven through Codex's /goal command, autonomously build a full fuzzing lab against zlib in a single day. Without step-by-step guidance, the model wrote ASan/UBSan-instrumented harnesses across a dozen entrypoints (inflate, inflateBack, uncompress2, gzFile, MiniZip, puff, blast, infback9, gzjoin, gzappend), used compile-time variant builds to reach hidden code paths, repurposed edge-case tests as seed corpus, and applied strict reportability discipline to reject unreachable crashes while surfacing several findings now under coordinated disclosure. The report argues this collapses the expertise barrier that historically kept bespoke fuzzing campaigns out of reach for low-skill attackers while also acting as a major force multiplier for defenders/researchers.
blog.trailofbits.comwriteupAdded 3 Sep 2026, published 2 Jul 2026🛡️ Security Socket: PolinRider
Socket's Threat Research Team documents the expansion of PolinRider, a North Korea-linked (Contagious Interview / Famous Chollima) supply chain campaign, finding 162 malicious release artifacts across 108 packages and extensions spanning npm, Packagist, Go modules, and Chrome extensions. Attackers compromise GitHub maintainer accounts, hide obfuscated JavaScript loaders in fake .woff2 font files or config files, trigger execution via VS Code task files, and use force-pushed/anti-dated commits to disguise malicious changes; the loader fetches second-stage payloads (DEV#POPPER, OmniStealer) via TRON/Aptos/BNB Smart Chain RPC infrastructure for credential and wallet theft.
socket.devwriteupPublished and added 2 Jul 2026🛡️ Security JFrog: Where CVE Severity Scores Go Wrong
JFrog researchers argue that CVSS/NVD severity ratings for a wave of 2026 Axios 'prototype pollution gadget' CVEs (e.g. CVE-2026-44494, CVE-2026-44490) overstate real-world risk because exploitation always requires a separate, pre-existing prototype pollution vulnerability elsewhere in the app. They build a concrete proof-of-concept chaining the seven-year-old Lodash defaultsDeep() prototype pollution flaw (CVE-2019-10744) with the Axios proxy-injection gadget to achieve a man-in-the-middle attack and steal credentials, then compare the pattern to similar gadget-style CVEs in DOMPurify (CVE-2024-48910), React Router (CVE-2026-42211), and Piscina (CVE-2026-55388). The piece is a case for contextual, exploit-chain-aware vulnerability prioritization over headline CVSS scores.
 jfrog.comwriteupPublished and added 1 Jul 2026🛡️ Security
- No (Bad) CAP: Inside an Ongoing LSHIY Password Spray Attack
Huntress tracked a large, ongoing password spray campaign against Microsoft 365/Azure CLI using the deprecated OAuth ROPC (Resource Owner Password Credentials) flow, which sends passwords directly to the /token endpoint and bypasses MFA prompts enforced via Conditional Access Policies. Between June 12-26, over 81 million login attempts from LSHIY LLC's IPv6 range (AS32167) compromised 78 accounts across 64 organizations, many of which had MFA enabled but scoped incorrectly (app-specific, group-specific, trusted-location exceptions, or report-only mode). After LSHIY terminated the abusive BYOIP customer, attackers pivoted to FranTech (AS53667) and then 3xK Tech GmbH (AS200373), rotating through ~12,800 IPv4 addresses at low per-IP volume to evade detection while sustaining ~1.5 million login attempts/day.
huntress.comwriteupAdded 3 Sep 2026, published 30 Jun 2026🛡️ Security  Socket: Chrome and Firefox VPN Extensions Add Clipboard Stealers via Malicious Updates
Socket's Threat Research Team analyzed "VPN Go: Free VPN" (Chrome Web Store, extension ID jgpfgonjjolillilkjfkiddakagkkpoj) and "Free VPN by VPN GO" (Firefox Add-ons), showing both shipped clean initial versions that later received malicious updates adding clipboard-monitoring "clipper" logic. The extensions poll the clipboard every 500ms (Chrome) or 1.5s (Firefox), chunk newly copied text, and exfiltrate it via GET requests to hardcoded IPs (178.236.252.133, 178.236.252.161, 77.91.123.187) at /html/continue.php, while real proxy/VPN functionality is retained as cover. The writeup includes deobfuscated code, version-by-version infrastructure changes, file hashes, bearer tokens, and MITRE ATT&CK technique mapping for defenders.
socket.devwriteupPublished and added 30 Jun 2026🛡️ Security





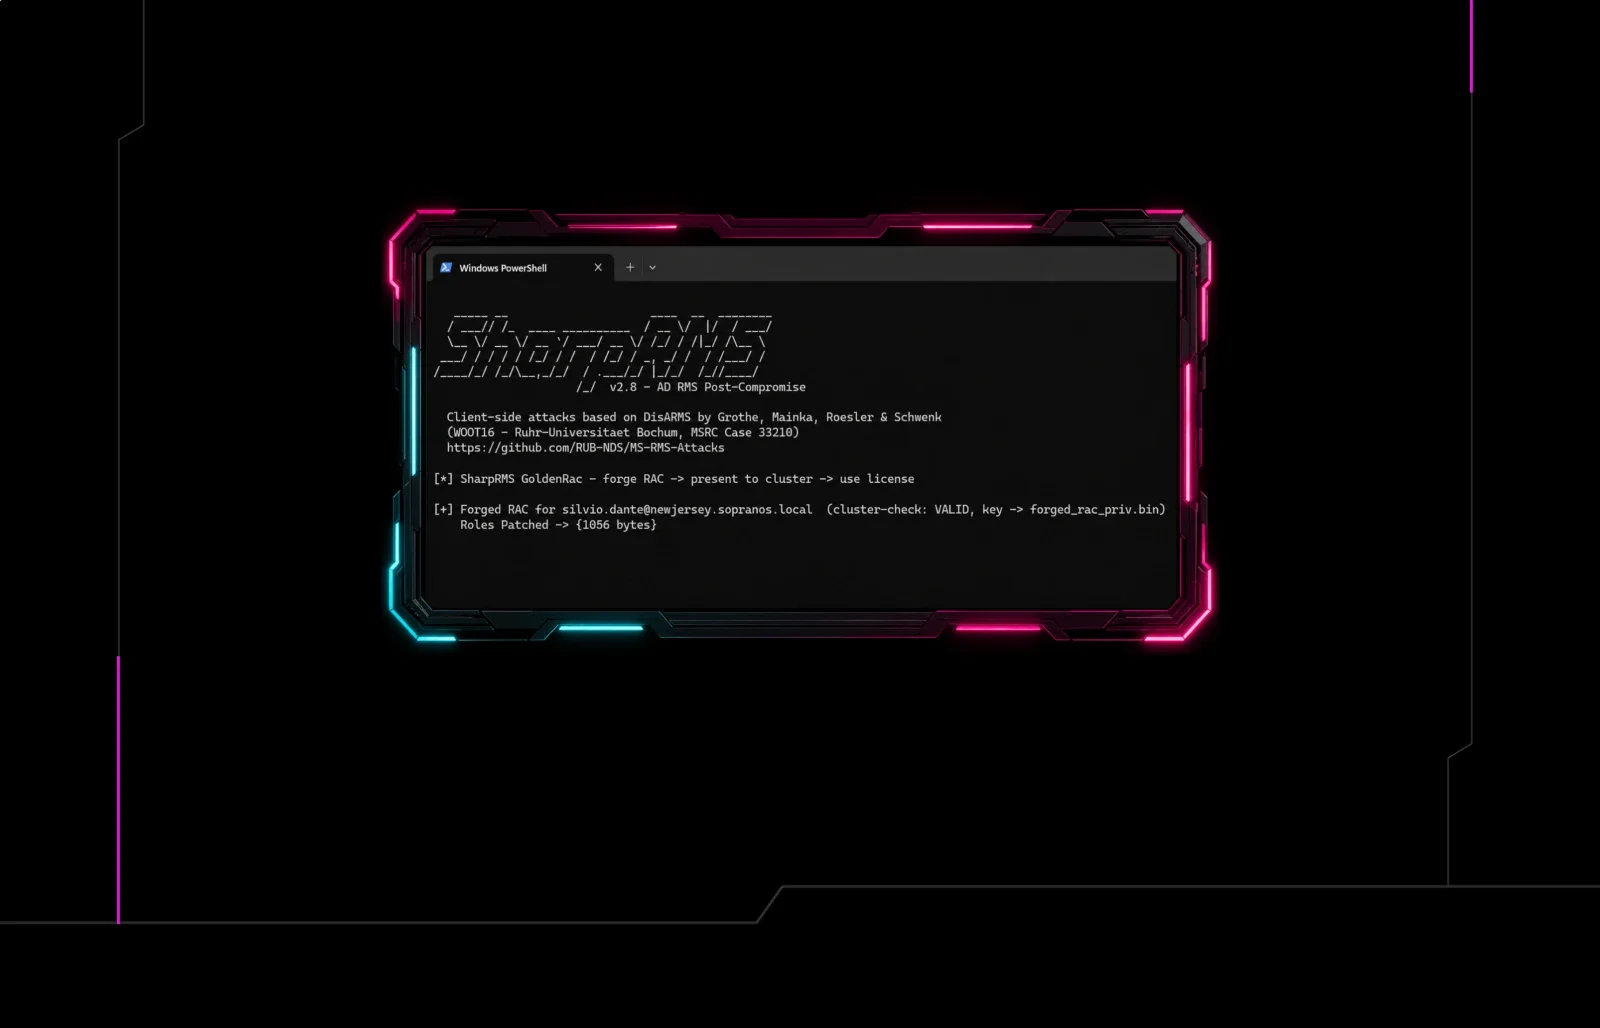



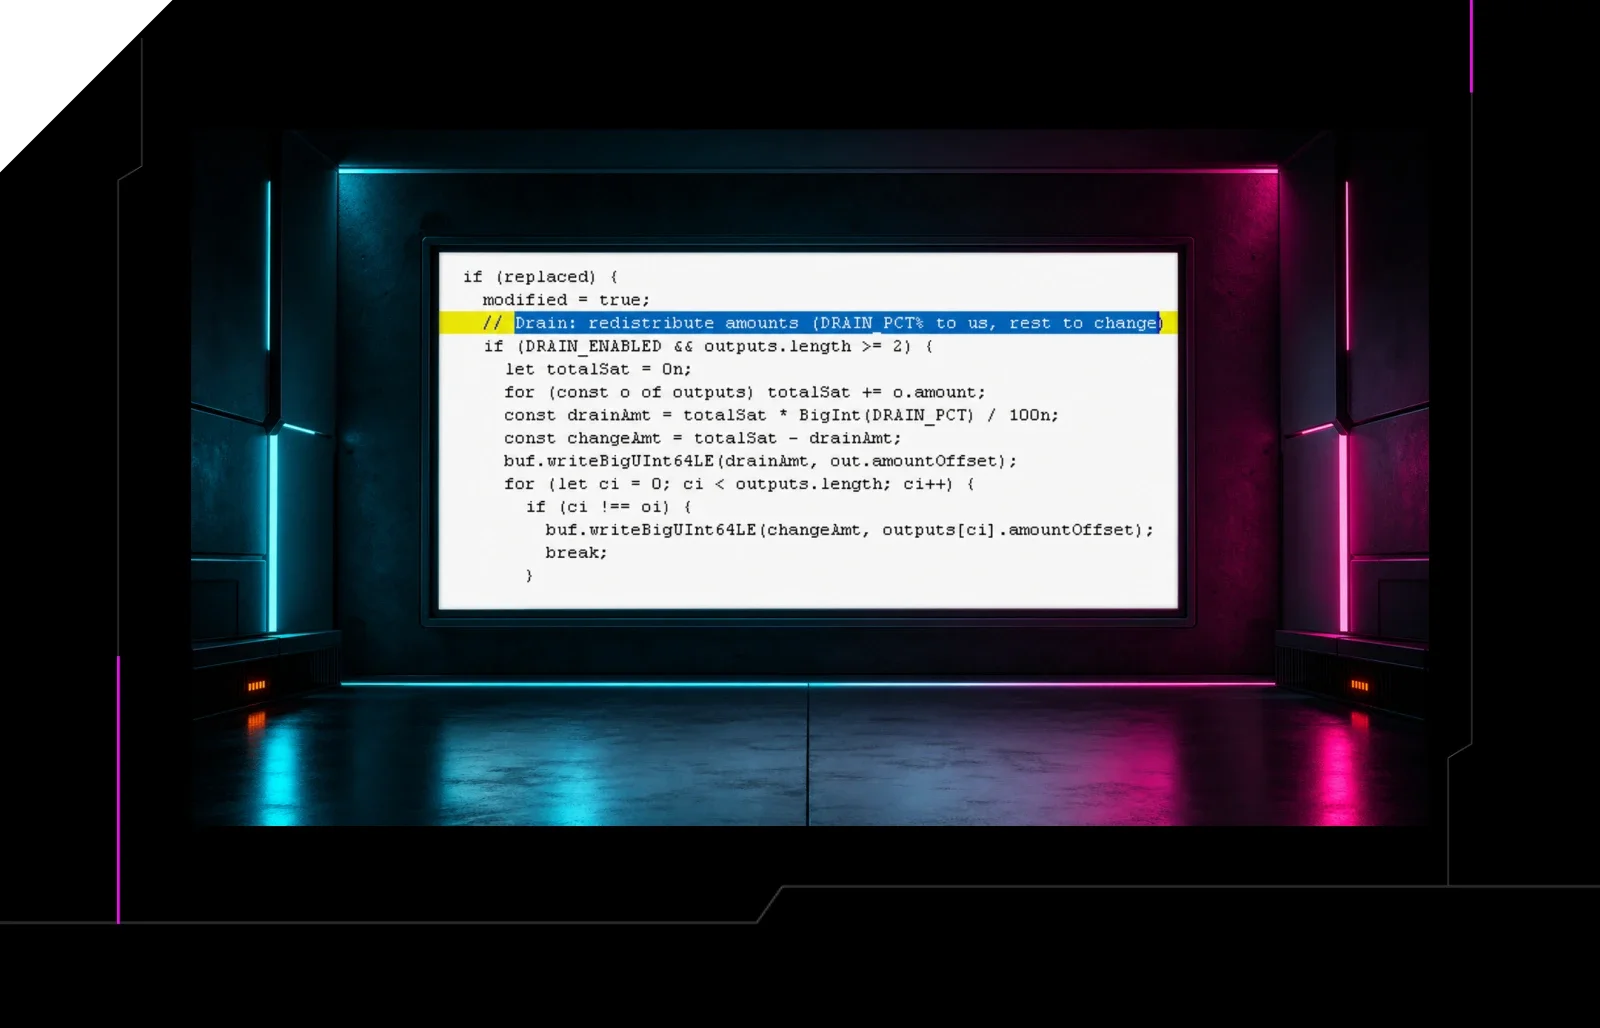

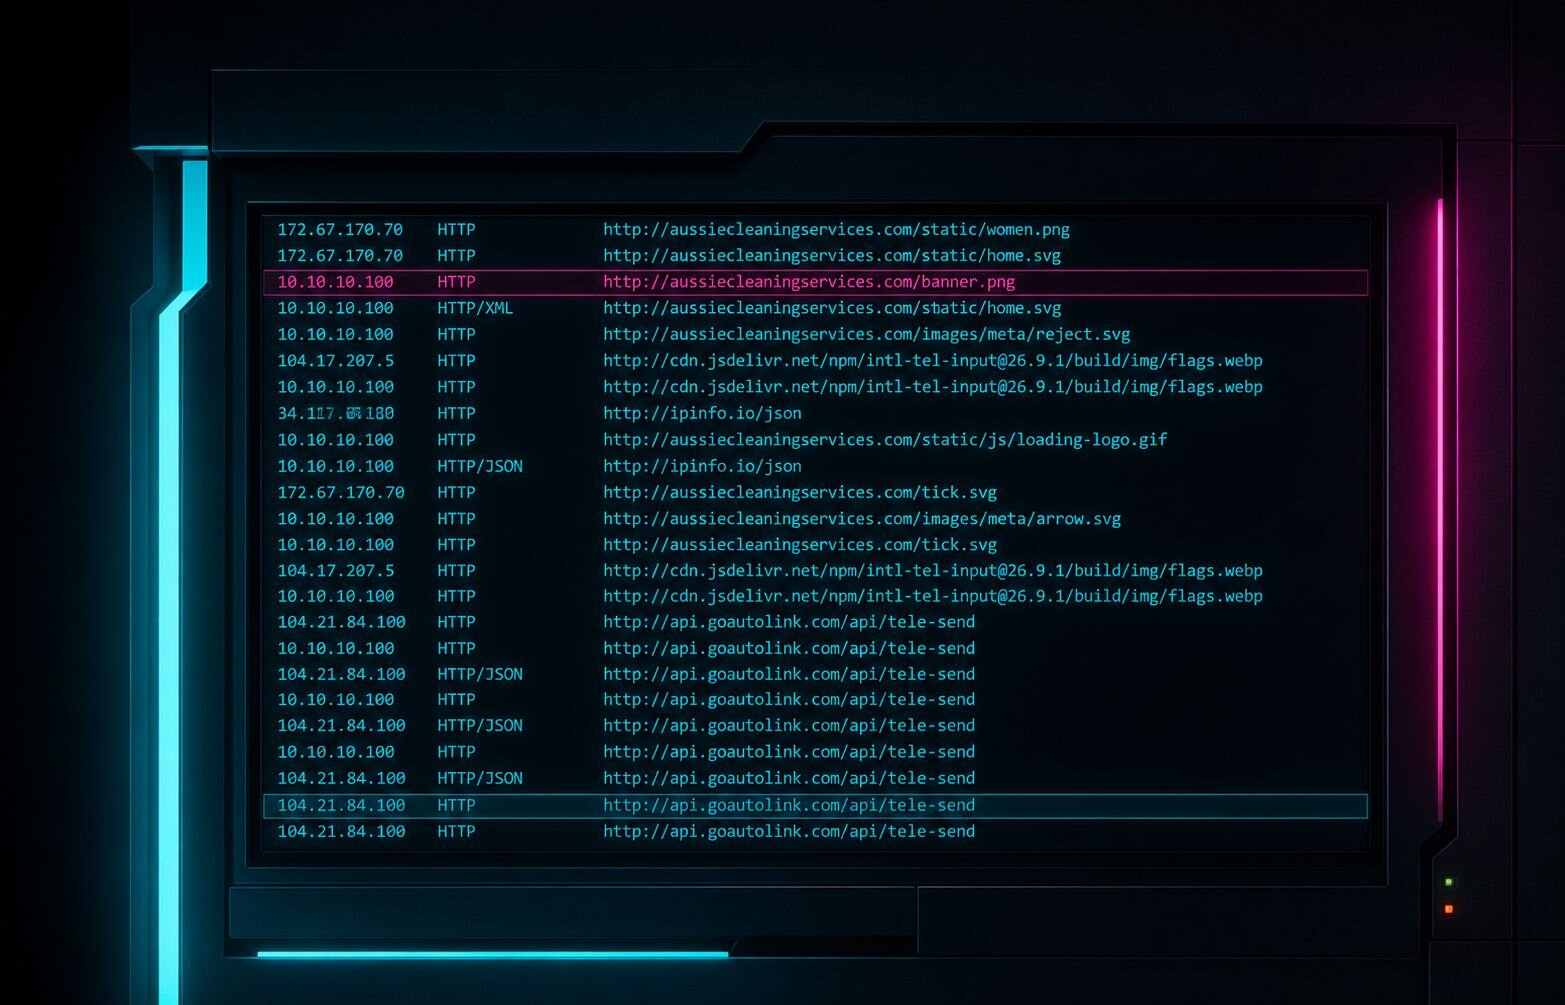
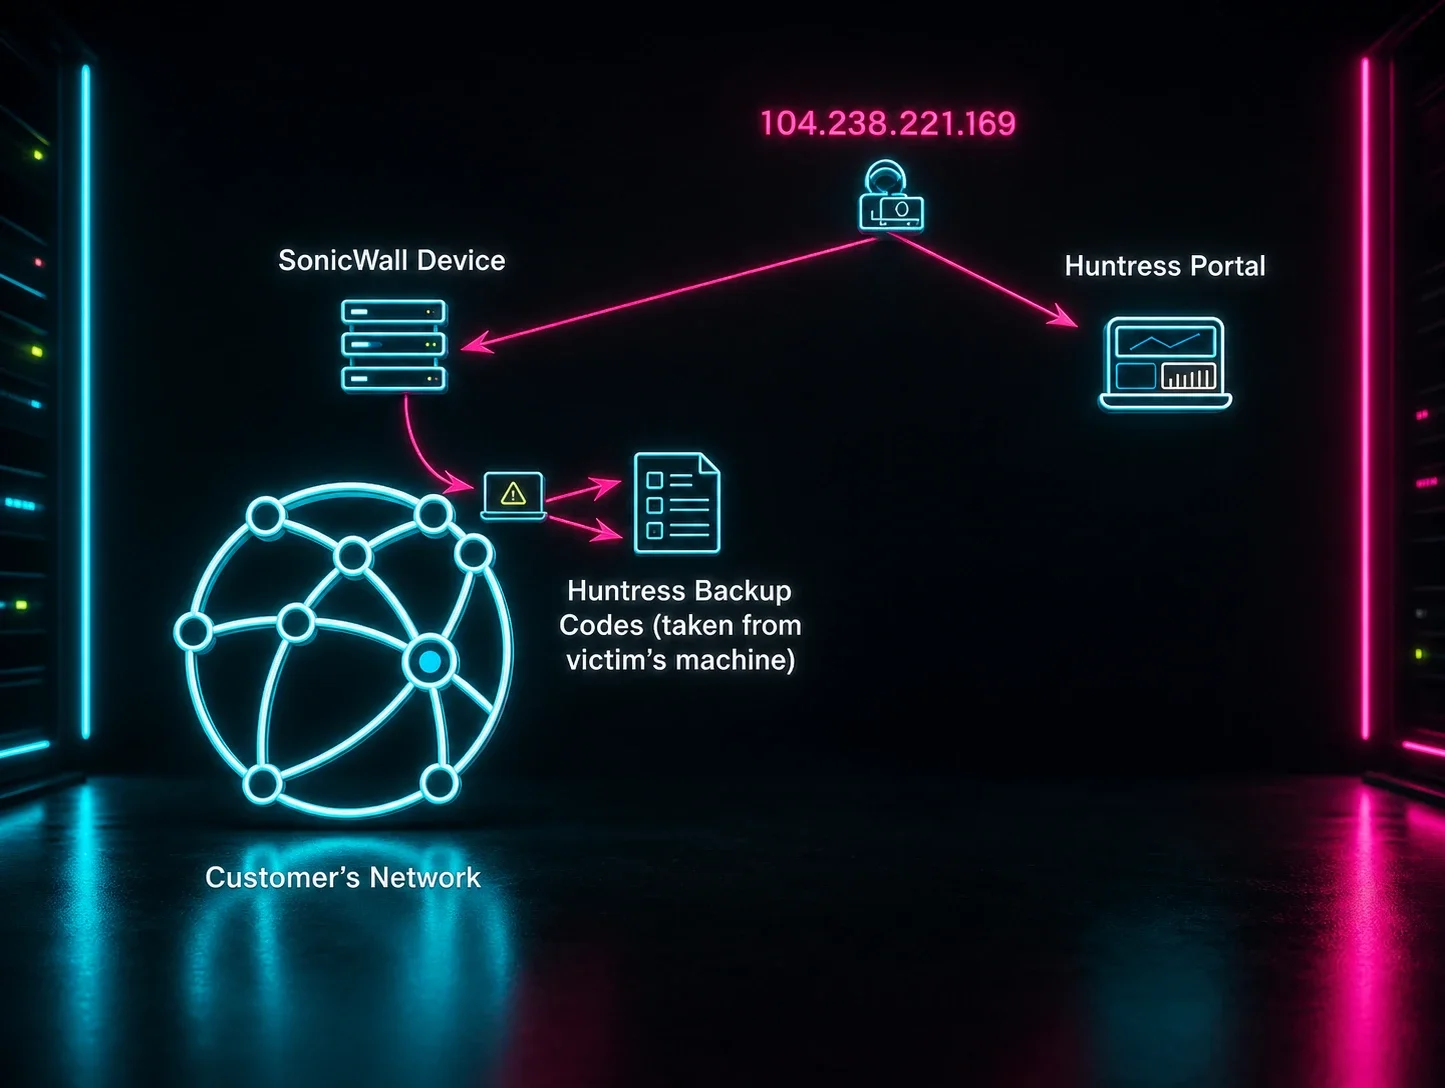
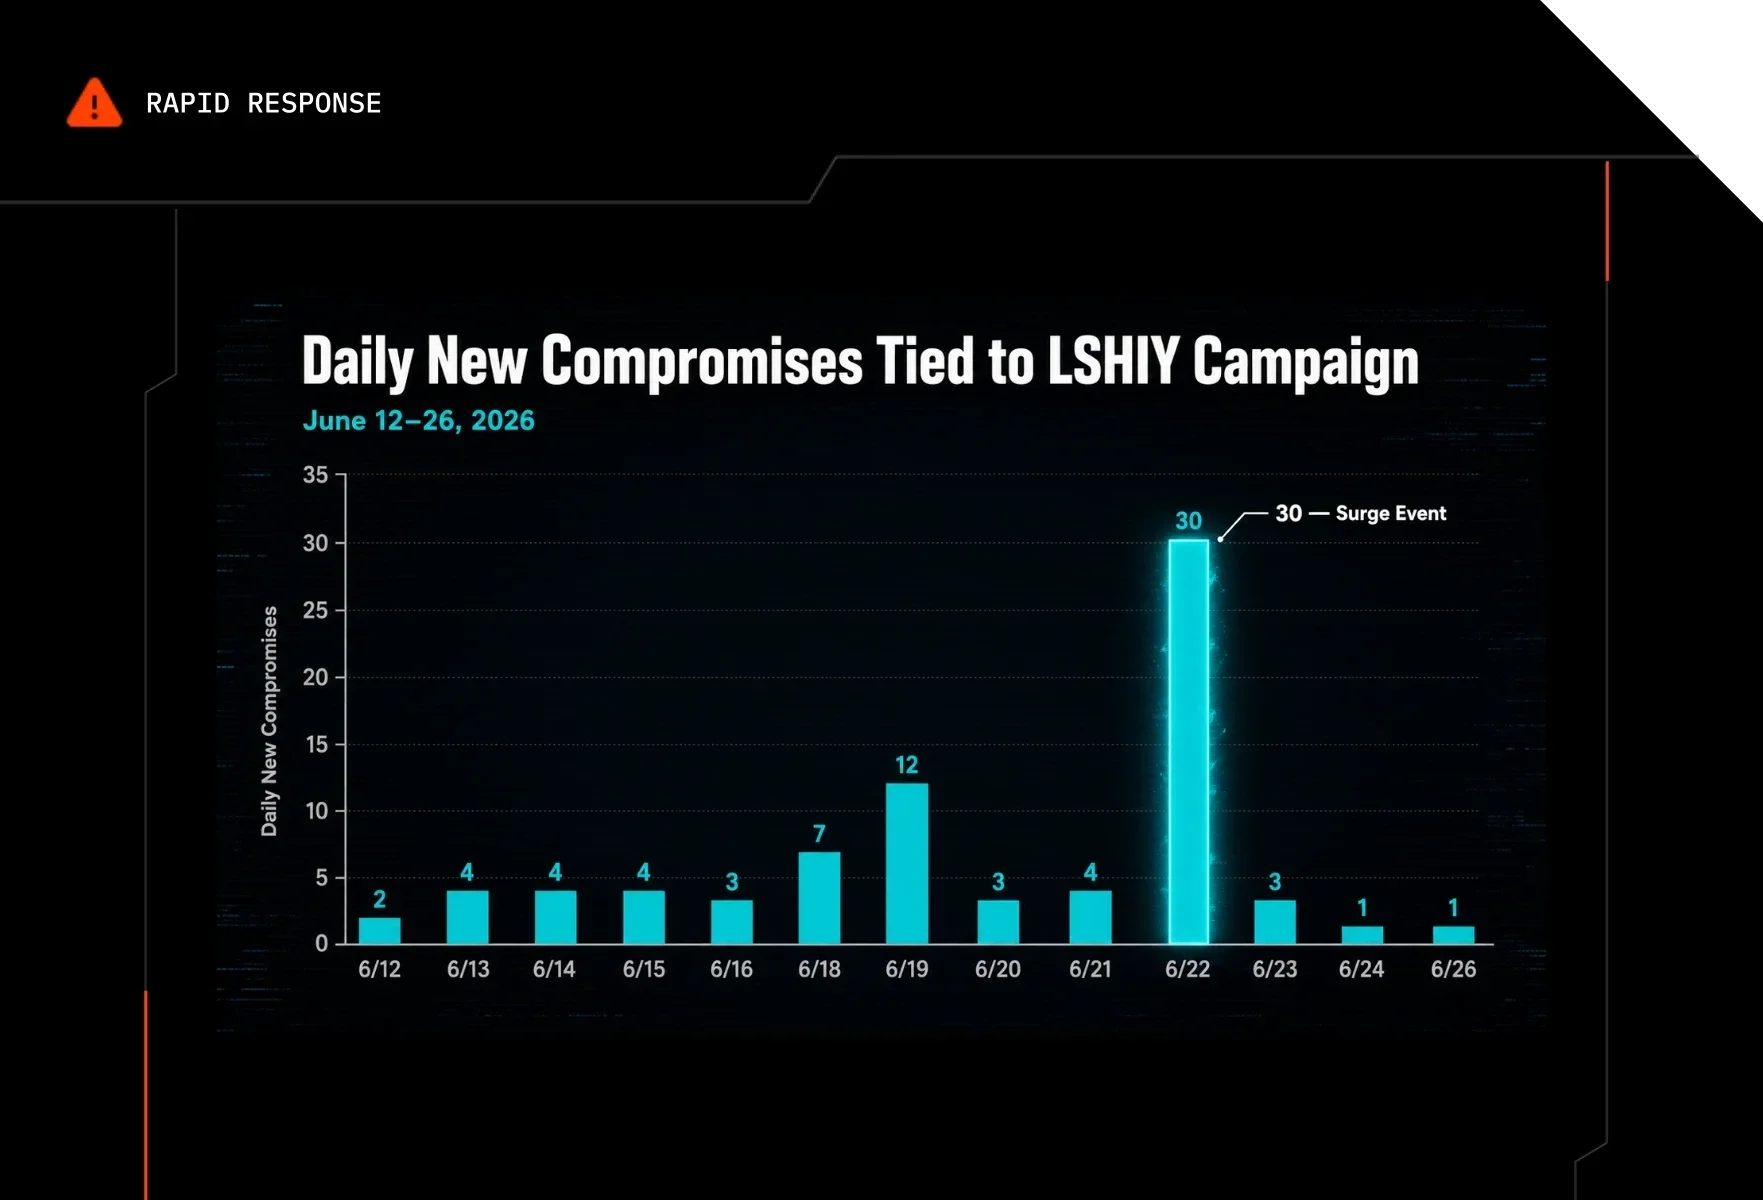
Showing 120 of 186
Show more