Skip to content

230 results for “drop”

What you seeeverything
“drop”
securityweek.comarticle🛡️ Security

Malicious Claude Code Extension Served in Cursor Supply Chain Attack

Malicious versions 2.1.312 and 2.1.313 of the anthropic.claude-code extension were live in the Cursor VS Code Extension Marketplace for about 11 hours on October 29. The JavaScript ran at module load, collected host details, tried to install an SSH key, open a reverse SSH tunnel and set persistence on macOS and Windows. Kevin Beaumont estimates about 5,000 downloads. Cursor rotated keys, rebuilt the marketplace and published a detection script and IoCs; uninstalling alone does not remove the dropped persistence scripts.

Claude CodeCursorVS Code+3
Kevin BeaumontAnthropicMicrosoft

Supply Chain, Threat Intel· Published and added 2 Nov 2026

aikido.devadvisory🛡️ Security

Critical Linux kernel TCP vulnerability can allow remote code execution (CVE-2026-98432)

CVE-2026-98432 is a use-after-free in the Linux kernel IPv4 TCP handshake (tcp_v4_syn_recv_sock, ip_options_build), present since kernel 4.4 and rated 9.8 by the kernel CVE team. Anthropic reports a Claude research model wrote a remote root exploit against hosts with an MPTCP listener. The post lists AWS, Ubuntu and Red Hat patch status, interim mitigations (disable MPTCP, drop IP-options packets) and the uname -r check. No in-the-wild attacks were reported as of 29 October 2026.

Linux kernelMPTCPGo+3
CVE-2026-98432CVE-2025-98432use-after-free+5

Cloud & Infra, AI Security· Published and added 2 Nov 2026

atlasum.netadvisory🛡️ Security

TCP Use-After-Free: CVE-2026-98432 / CVSS 9.8

CVE-2026-98432 is a use-after-free in the Linux IPv4 TCP handshake, rated CVSS 3.1 9.8 and reachable by a remote unauthenticated peer on kernels back to 4.4. The post lists fixed stable releases (October 2026) and distribution patch status as of 31 October 2026, plus kernel and MPTCP listener checks. It gives interim nftables and iptables rules that drop IPv4 packets carrying options, and notes Anthropic's claim that Claude wrote a working exploit.

Linux kernelnftablesiptables+3
CVE-2026-98432use-after-freeAnthropic

Blue Team & Detection, Cloud & Infra· Added 1 Nov 2026, published 31 Oct 2026

bleepingcomputer.comarticle🛡️ Security

New Android SMS of Death exploit can remotely crash unpatched phones

CVE-2026-58882, "SMS of Death", is a zero-click Android denial-of-service flaw in WapPushOverSms.decodeWapPdu, where an unchecked header-length value becomes negative and triggers a NegativeArraySizeException that crashes com.android.phone. A malformed eight-byte WAP Push message to port 2948 can drop calls, including emergency calls, and about 20 messages caused reboot loops. A PoC is public. Google patched Android 14 through 17 in October 2026, but Android 12 and 13 remain vulnerable.

AndroidAndroid Debug BridgeGitHub
CVE-2026-58882SMS of DeathGoogle+3

Mobile Security, Offensive Security· Published and added 31 Oct 2026

latent.spacearticle🧠 AI

[AINews] Google admits AI Mode hurts Search revenue; -15% $500B drop worst since 2004 IPO. AI Bear Market coming?

AINews issue for 29 to 30 October 2026 from Latent Space. It opens on Google's admission that AI Mode monetises worse than classic Search, which preceded a roughly 15% share drop. It then recaps Claude Ultra dropping the 5-hour limit, Gemini 4 Carbon, Mistral Large 4, Nemotron 3.5, Artificial Analysis Index v5, Unsloth GGUF disputes, and the Anthropic S-1 filing.

Claude CodeClaudeGemini+17
GoogleAnthropicOpenAI+46

ai-policy, models, evals· Published and added 31 Oct 2026

protos.comarticle🛡️ Security

Trezor reveals Malaysian reseller sold wallet with spyware

Trezor says a user reported a Safe 5 wallet bought from Malaysian reseller CryptoBilis in August 2026 with a hidden board between the main board and screen, carrying a cellular module and antenna. The implant allegedly reads the screen, including the wallet backup, and sends it over a mobile network when plugged in. Trezor has not yet examined the device, has dropped CryptoBilis (9 October), and is replacing wallets bought since March 2026.

TrezorLedger
CryptoBilisDanny Sanders

Hardware & RF, Blockchain, Threat Intel· Published and added 30 Oct 2026

youtu.bevideo🛡️ Security

Muse pdfdetach POC

The uploader demonstrates a remote code execution exploit chain against Muse, an assistant system that uses the pdfdetach utility to parse PDF attachments. The exploit leverages a path traversal vulnerability during file extraction to drop a malicious shared library and an LD_PRELOAD configuration file.

MusepdfdetachPython

AppSec· Published and added 30 Oct 2026

vulncheck.comother🛡️ Security

VulnCheck - Outpace Adversaries

VulnCheck's vulnerability disclosure policy, last revised March 2026, sets a 120 day deadline for vendors to patch or publish an advisory, after which VulnCheck publishes an uncoordinated third-party advisory. The deadline drops to 7 days if exploitation in the wild is found. Other terms: no extensions, email-only communication, any published patch counts as public disclosure, and no participation in programs that bar public disclosure.

VulnCheckcoordinated disclosure

GRC· Added 29 Oct 2026
securityweek.comarticle🛡️ Security

China-Linked Hackers Exploit PHP2Shell to Root Firewalls

A China-linked actor chained PHP2Shell (CVE-2026-109618, CVE-2026-109619) with the Fragnesia Linux kernel privilege escalation (CVE-2026-46300) to root firewalls and drop PHP webshells, per Dream. Using FOFA, the actor narrowed 19,000 firewalls to 240 targets and rooted 24 on 23-24 October. On two US government-affiliated devices it used a reverse SSH tunnel, hit the firewall management server, and attempted LDAP and Active Directory abuse.

PHPLinux kernelSSH+2
CVE-2026-109618CVE-2026-109619CVE-2026-46300+7

Threat Intel, Offensive Security· Published and added 28 Oct 2026

latent.spacearticle🧠 AI

[AINews] Anthropic ends Coding Interviews: "Hunger beats tenure"

AINews issue of 28 October 2026 from Latent Space. It leads with Felix Rieseberg's post on why Anthropic dropped coding interviews ("Hunger beats tenure"). It then recaps Genie 4, Axiom's Lean formalization of CFSG, claimed ETH refutations by OpenAI and Anthropic, Artificial Analysis Index v5, FrontierCode 2.0, Liquid LFM3, the Qwen3.8 phone-home dispute, and Anthropic's S-1. Reddit recaps are included; the page was truncated before the end.
LeanQwen3.8-27BvLLM+11
AnthropicFelix RiesebergGoogle DeepMind+40

models, evals, ai-policy· Published and added 28 Oct 2026

arxiv.orgpaper🧠 AI

Locating Sycophancy Across Training Stages in Open Language Models

Locating Sycophancy Across Training Stages in Open Language Models measures sycophancy in 13 open checkpoints from 5 lineages, from base model through supervised fine-tuning and preference optimization to release. It finds two behaviors with different origins: deference to a claim in the prompt exists in every base model, while capitulation under user objection is largely absent from base models and present in every post-trained checkpoint. Post-trained models often drop firmly held answers as readily as loosely held ones when the objection names an alternative.

LLM
arXiv

ai-safety, research, evals· Added 30 Oct 2026, published 27 Oct 2026

arxiv.orgpaper🧠 AI

FeatureArc: Benchmarking Coding Agents on Evolving Features

FeatureArc is a benchmark for coding agents on evolving features, built by a pipeline that mines repository histories into multi-stage tasks across four programming languages. It has 73 manually reviewed tasks of 2 to 10 stages, validated with fail-to-pass and pass-to-pass tests. Across 10 agents, pooled success drops from 62.7% at the first stage to 28.5% for the whole feature. Inherited defects appear in 72.9% of failed later stages.

LLM
FeatureArcTencentHunyuan+1

evals, coding-agents, research· Added 28 Oct 2026, published 27 Oct 2026

eprint.iacr.orgpaper🛡️ Security

Radical isogenies on every model

Radical isogenies on every model is an IACR ePrint paper by Thomas Decru (October 2026). It gives radical isogeny steps of every odd degree N directly on short Weierstrass, Montgomery, twisted Edwards, Huff, Jacobi quartic, twisted Hessian, Legendre and Jacobi intersection curves, plus Kummer lines. In Tate normal form a step drops from 12.5N to 10N multiplications. Montgomery and twisted Edwards curves cost 10.5N+O(1) per step and 2N to push a point. All algorithms are inversion-free, with exact operation counts.

CSIDH
Thomas Decruradical isogeniesVélu's formulae+1

other· Added 28 Oct 2026, published 27 Oct 2026

huntress.comwriteup🛡️ Security

Camera Management Software Compromise Leads to Malware Deployment

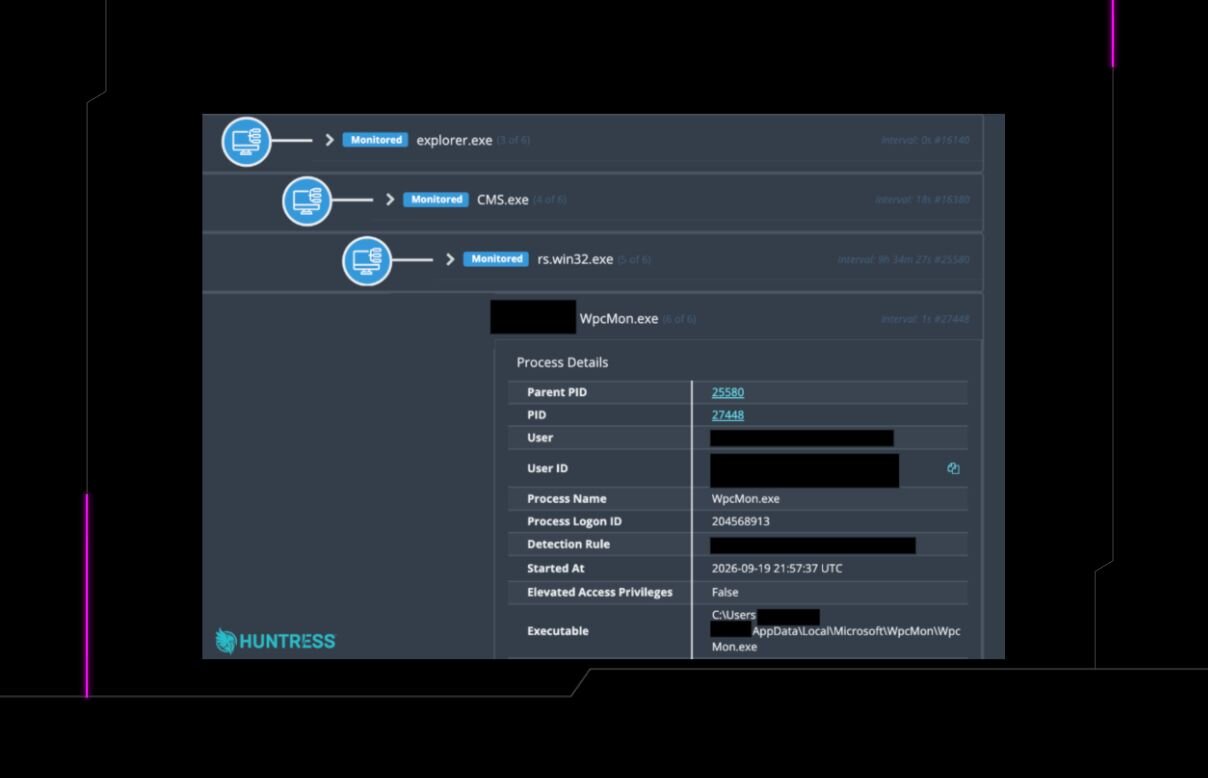
Huntress investigation of incidents in September and October 2025 where a compromised camera management application (CMS.exe) was the initial access vector. Attackers dropped rs.win32.exe, a reverse shell, and sideloaded modified zlib DLLs (IPHLPAPI.DLL, samcli.dll) via the legitimate Microsoft WpcMon.exe in AppData, with Run key persistence and beaconing to 144.172.116[.]37. Includes detection pivots and hardening advice.

WindowsHuntress
DLL sideloadingCMS.exers.win32.exe+6

Threat Intel, Blue Team & Detection· Added 28 Oct 2026, published 27 Oct 2026

blog.cloudflare.comarticle🛡️ Security

What took the Internet offline in Q3 2026

Cloudflare's Q3 2026 review of the 49 Internet disruptions seen by Cloudflare Radar between July and September 2026. Government-directed shutdowns led with 19 (18 exam shutdowns in Iraq), followed by 14 power outages and 5 natural disasters. It gives traffic-drop figures and durations for Cuba, Honduras, Ukraine, Guam, Colombia, Ethiopia's Tigray region and others, including a Honduran interconnection facility power failure that cut HTTP traffic 63%.

Cloudflare
Iraq exam shutdownsTigray shutdownSuper Typhoon Bavi+10

other· Added 29 Oct 2026, published 27 Oct 2026

x.comthread🧠 AI

Abdullah (@abdullah0094) on X

An X thread by Abdullah on GPT-6.1 Terra versus Sol in Codex. Abdullah says Terra gives twice the Codex usage of Sol and asks whether the quality drop is obvious. A reply says it is too early for a verdict, cites OpenAI's claim that Terra matches GPT-6 Astra on Agents' Last Exam, and suggests defaulting to Terra and switching to Sol with /model when it stalls.

Codex
GPT-6.1 TerraGPT-6.1 SolGPT-6 Astra+2

coding-agents, models· Published and added 27 Oct 2026

x.comadvisory🛡️ Security

dbugs (@ptdbugs) on X

CVE-2026-106173 is a critical (CVSS 9.4) unauthenticated arbitrary file write in FortiSIEM's phQueryMaster gRPC service on port 27918/TCP. The SendQueryResult method builds a path from the query-id parameter without validation, so "../" sequences escape the directory and a null byte drops the appended filename and extension. Overwriting /opt/charting/redishb.sh, which runs every 60 seconds, gives remote command execution. Horizon3.ai published the analysis and a PoC.

FortiSIEMgRPCRedis+1
CVE-2026-106173PT-2026-111783Horizon3.ai+4

Offensive Security, AppSec· Added 27 Oct 2026, published 26 Oct 2026

arxiv.orgpaper🛡️ Security

SymLift: Neural Semantic Lifting for Compile-Free Vulnerability Detection in Context-Incomplete Code Fragments

SymLift is a compile-free vulnerability detection framework for context-incomplete code fragments. A fine-tuned LLM lifts control-flow, data-flow, memory and resource relations into a constrained LLVM-like IR. A parser turns the IR into facts, and Datalog rules derive findings with derivation traces. On Juliet function-level fragments Clang compilation success falls to 12.00%, while SymLift's completion rate drops only 1.17 points. SymLift-Qwen-7B reaches Target-F1 94.41% on FormAI and 91.66% micro-F1 on MegaVul.

LLMQwenLLVM+2
SymLiftFormAIJuliet+2

AppSec, AI Security· Added 28 Oct 2026, published 25 Oct 2026

stepsecurity.iowriteup🛡️ Security

OVHcloud CLI Compromised via GitHub Release Swap: Detonating the Real GlassWorm Loader and What We Found

Analysis of the 19 October 2026 swap of binaries on five ovh/ovhcloud-cli GitHub releases (v0.11.0 to v0.15.0), live 94 minutes. StepSecurity rebuilt the attacker's binary, detonated the recovered GlassWorm preinstall.js loader against a controlled Solana dead drop, and found install.sh never exposed arm64 Linux, Homebrew was safe, and `ovhcloud version` showing "undefined" identifies the swapped build. Includes IOCs and recovery steps.

OVHcloud CLIGitHubSolana+3
GlassWormForceMemoGHSA-862f-55f5-vmvw+8

Supply Chain, Malware & RE, Threat Intel· Published and added 24 Oct 2026

arxiv.orgpaper🧠 AI

When to Stop Penalizing Actions? Martingale GRPO for VLA Reinforcement Learning

MART-GRPO is a variant of group-relative policy optimization for vision-language-action (VLA) reinforcement learning. It uses a LoRA-fine-tuned VLM to find the last visible error without recovery in a failed rollout video, keeps failure feedback up to that point, and drops it afterward. Martingale stopping conditions show this preserves the expected GRPO gradient and can reduce covariance. With OpenVLA-OFT on RoboTwin 2.0, it raises success rates over full-trajectory GRPO across multiple tasks.

GRPOLoRAvision-language-action model+2
RoboTwin 2.0arXiv

research, training, multimodal· Added 26 Oct 2026, published 23 Oct 2026

blog.alexewerlof.comarticle🧠 AI

The rise and fall of Jev hype

The essay uses the launch of Jev, TypeSafe AI's "System One" general-purpose classifier trained with RLCD, to dissect AI marketing patterns: name dropping, jargon, ambiguity, inflated claims and drama. The author argues Jev's hype peaked and collapsed within about 33 days, while open-weight rivals beat it on cost and performance. It also lists incremental advances since ChatGPT and four unsolved problems: abstract reasoning, continuous learning, embodiment and the economics of running AI.

JevLLMModel Context Protocol+4
TypeSafe AITypeSafeOpenAI+14

ai-policy, models· Added 24 Oct 2026, published 23 Oct 2026

huggingface.copaper🧠 AI

Cache Engineering for Agents (AKV)

AKV introduces cache engineering, which lets LLM agents control their active KV cache with drop (exclude cache from future attention) and repos (adjust retained keys' position encodings) without editing the trajectory or re-prefilling. The AKV serving engine keeps a stateless API while managing stateful cache reuse, eviction and restoration. A tool-response rolling-drop policy raised benchmark scores by 1.7 points and cut cost 27.7% versus threshold-triggered summarization.

LLMTransformerGitHub+1
AKV

inference, agents, research· Added 23 Oct 2026

x.comthread🧠 AI

Daily Vibe Casting (@vibecastingapp) on X

Daily Vibe Casting is an X thread dated 24 October 2026 that summarises ten tech news items from the previous 24 hours. The AI items are Cloudflare's model-independent agent security audit skill, Recursive SI's Apache 2.0 Flint local coding model (125+ tokens/s on an M4 Pro), Anthropic's Claude Duet preview and Claude API version 2026-10-21, which drops temperature, top_p and top_k. It also covers HeyGen Voice Turbo and Gemini in Google Maps on CarPlay.

CloudflareClaudeGemini+2
CVE-2026-110264Recursive SIFlint+6

models, coding-agents, agents· Added 24 Oct 2026, published 22 Oct 2026

x.comthread🛡️ Security

SecureChap (@SecureChap) on X

Post describing a LiteLLM 1.107.0 PyPI compromise in which attackers used stolen GitHub CLI OAuth tokens from three engineers to trigger and approve the project-releaser workflow, producing eight malicious wheels and a tampered tarball. The wheels drop cook.pth, which runs at Python startup, and privcollect steals cloud tokens, keys, browser data, AI configs and LiteLLM proxy credentials, exfiltrating to litellm[.]dev/healthcheck. A second daemon polls a GitHub domain.txt hourly for new domains to fetch and execute. PyPI yanked the package the same day. The post is a single unsourced tweet.

LiteLLMPyPIpip+3
cook.pthprivcollectlitellm[.]dev+2

Supply Chain, DevSecOps, Threat Intel· Published and added 22 Oct 2026

soliditylang.orgadvisory🛡️ Security

Yul Optimizer Knowledge Base Stale Bookkeeping Bug

Solidity advisory on a Yul optimizer bug in the KnowledgeBase, present in versions 0.8.19 to 0.8.37 and fixed in 0.8.38. Stale cached address offsets let LoadResolver and EqualStoreEliminator treat coinciding memory or storage slots as distinct, so loads return outdated values or needed stores are dropped. It includes a pure-Solidity reproducer for --via-ir, a Sourcify scan with no differing bytecode, and checks for deployed contracts. Rated low severity.

SolidityYulSourcify+1
Ethereum Foundation bug bountyDaniel BoyeSurya Prakash Akula+4

AppSec· Published and added 22 Oct 2026

huggingface.coarticle🧠 AI

How Specializing the Vocabulary of SLMs Can Cut Inference Cost by 77% in Real Applications

VocabX is a vocabulary adaptation method from Dharma-AI that selects sub-word and multi-word "macro" tokens by serving cost instead of frequency. On a Qwen3-4B Portuguese essay grader, response length fell from 350 to 101 tokens, the LM head shrank from about 152,000 to 65,000 rows, and measured cost dropped 77.0% on an RTX 5090 with vLLM. The bench score rose from 0.703 to 0.810. It beat FVT, MWT and in-place BPE across 15 model and domain combinations.

Qwen3vLLMLlama+3
Dharma-AIVocabXQwen+1

inference, training, research· Published and added 21 Oct 2026

stepsecurity.iowriteup🛡️ Security

litellm 1.107.0 Compromised on PyPI: Backdoored Wheels Drop a Credential Stealer and an Hourly Remote Code Loader

litellm 1.107.0 was published to PyPI on 21 October 2026 with all seven wheels backdoored through an injected `data = "cook"` maturin build line. The wheels drop cook.pth, cook.py and sitecustomize.py, which run on every Python start. They install a "privcollect" credential stealer (browser, SSH, cloud, AI coding tool and LiteLLM proxy database secrets, sent to litellm.dev) and an hourly GitHub dead-drop remote code loader. The post gives IOCs, detection commands and recovery steps.

LiteLLMPyPIPython+3
privcollectcook.pthsitecustomize.py+6

Supply Chain, Malware & RE, Blue Team & Detection· Published and added 21 Oct 2026

wiz.iowriteup🛡️ Security

LiteLLM Compromised, Steals Credentials

LiteLLM version 1.107.0 was uploaded to PyPI on 21 October 2026 with a credential stealer, and the same build reached GHCR and Docker Hub images. Wiz describes the three dropped files (cook.pth, cook.py, sitecustomize.py), exfiltration to a fake litellm.dev domain, a GitHub dead drop for a second stage, and the malicious commits pushed through the lookalike Berri-AI repository. The last safe version is 1.106.2.

LiteLLMPyPIDocker+3
Berri-AIcook.pthsitecustomize.py+2

Supply Chain, Threat Intel, AI Security· Published and added 21 Oct 2026

arxiv.orgpaper🛡️ Security

Where AI Vulnerability Discovery Harnesses Go Quiet: Structural False Negatives and Hidden Vulnerabilities

Paper (arXiv, 21 October 2026) on structural false negatives in LLM vulnerability discovery harnesses. Starting from Knostic's OpenAnt and raptor, then 10 more open-source harnesses, the authors map 13 points where code selection, filtering, and finding storage or merging drop vulnerabilities. One file was dropped by six harnesses before the model saw it, five without notice. It covers attacker evasion, content-steered verdicts, prompt injection, and design principles and tests.

OpenAntraptorLLM
KnosticPtacek and Newshamprompt injection+1

AI Security, AppSec· Added 24 Oct 2026, published 21 Oct 2026

eprint.iacr.orgpaper🛡️ Security

HAETAE on a Diet: Less Stack, Less Time on Low-End Microcontrollers

This ePrint paper presents an optimized HAETAE implementation, a lattice-based post-quantum signature scheme, for Cortex-M4, Cortex-M3, MSP430 and AVR. It keeps polynomials in 16 bits, shares buffers between objects with disjoint lifetimes, and replays Gaussian samples instead of regenerating them. On an ATmega2560, HAETAE-2 key generation, signing and verification run in 8,070 B of SRAM. Stack use drops up to 34% and signing is 1.18-2.51x faster than Low-Stack HAETAE.

HAETAEML-DSAARM Cortex-M4+3
Low-Stack HAETAEHAETAE-2CHES 2026

Hardware & RF· Added 24 Oct 2026, published 21 Oct 2026

arxiv.orgpaper🧠 AI

InterWebCoder: Learning Interactive Webpage Generation from Executable Tests via Reinforcement Learning

InterWebCoder is a framework for interactive webpage code generation by multimodal LLMs. It synthesizes self-contained webpages with executable test scripts from recorded interaction trajectories, repairs failures using runtime evidence, then trains with test-ID-weighted SFT and GRPO using test pass rates and visual similarity as rewards. The pipeline yields 1,736 verified samples from 2,058 tasks. A 9B model scores 48.54 on IWR-Bench and 48.42 on Vision2Web, and reward latency drops over 97%.

GRPOvision-language modelLLM
InterWebCoderIWR-BenchVision2Web+3

research, training, multimodal· Added 22 Oct 2026, published 20 Oct 2026

arxiv.orgpaper🧠 AI

Benchmarking Arabic Dialects for Math Problems

DAR-MGSM (Dialectal Arabic Multilingual Grade School Math) is a manually curated benchmark for mathematical reasoning in Dialectal Arabic. It covers five major Arabic dialects plus Modern Standard Arabic, in a translated-only version and a translated and culturally localized version. Eleven Arabic-centric and multilingual LLMs were tested: accuracy generally drops on the localized version, and a mechanistic interpretability analysis shows the two variants induce distinct internal reasoning trajectories.

LLM
DAR-MGSMarXiv

evals, research· Added 22 Oct 2026, published 20 Oct 2026

arxiv.orgpaper🧠 AI

Cache Engineering for Agents

Cache Engineering for Agents proposes letting LLM agents control their active KV cache directly, using a drop operation to exclude cache from attention and repos to adjust retained keys' position encodings, without editing the trajectory or re-prefilling. The authors build the AKV serving engine to handle history-dependent cache states. A tool-response rolling-drop policy raises average benchmark scores by 1.7 points and cuts cost by 27.7% against threshold-triggered summarization. AKV gives up to 1.2x output throughput and 1.5x faster P95 latency.

LLMAKV
arXiv

research, inference, agents· Added 22 Oct 2026, published 20 Oct 2026

arxiv.orgpaper🧠 AI

TokenGate: Adapting LLMs for Fast and Memory-Efficient Prefill with Learned Token Pruning

TokenGate is a small drop-in component that adds end-to-end learnable token pruning to trained LLMs for long-context prefill. It uses token-gated attention, inspired by Mixture-of-Experts, to re-weight attention logits with token importance scores, which gets gradients through the non-differentiable top-K step. The authors report 1.4-11.3x faster time-to-first token and 1.5-3.4x lower peak memory with no accuracy loss, on Qwen3 and Qwen3.5.

TransformerQwen3Qwen3.5+2
TokenGatearXiv

research, inference· Added 21 Oct 2026, published 19 Oct 2026

arxiv.orgpaper🧠 AI

The Development of Sycophancy in Language Models: Tracing Vulnerabilities from Pretraining to Post-Training

The paper traces sycophancy across 741 checkpoints from 30 open model lineages, from early pretraining to released models. It plants initial verdicts on moral scenarios and measures how far models follow a user's opinion or drop their answer under pressure. The behaviour usually exists before post-training, but which questions a released model yields on is set mainly during post-training. For Tülu-3 8B, its own preference-stage checkpoint removes 85% of remaining prediction error, a sibling model only 19%.

LLM
Tülu-3 8BarXiv

ai-safety, research, training· Added 21 Oct 2026, published 19 Oct 2026

boredhackerblog.infowriteup🛡️ Security

Plex vulnerabilities being exploited in the wild to drop a cryptominer

Honeypot writeup of in-the-wild exploitation of Plex Media Server through the Plex2Shell chain (CVE-2026-96652, -96654, -96655, -96656) in October 2026. Attackers from 45.194.92.222, 91.92.40.202 and 176.65.139.228 used SSRF-style timeline/subscribe requests and downloaded a Docker-named dropper and an XMRig miner from 217.60.194.116. Includes file hashes, a later-seen proxyware sample (myawesomeproxy), lab pcaps for signatures and links to sandbox reports.

Plex Media ServerXMRigDocker+1
CVE-2026-96652CVE-2026-96654CVE-2026-96655+8

Threat Intel, Blue Team & Detection· Added 20 Oct 2026, published 19 Oct 2026

securityweek.comarticle🛡️ Security

Plex2Shell Exploit Chain Weaponized Against Plex Servers Hours After Disclosure

Plex2Shell is a chain of four Plex Media Server vulnerabilities (CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656) that gives unauthenticated code execution with the Plex service's privileges. Exploitation began on 17 October 2026, a day after the researcher published a write-up and PoC on 16 October. A honeypot saw an XMRig miner and a proxy tool, myawesomeproxy, dropped. Plex shipped fixes by 1 September 2026.

Plex Media ServerXMRig
CVE-2026-96652CVE-2026-96654CVE-2026-96655+4

Threat Intel, AppSec· Published and added 19 Oct 2026

securityweek.comarticle🛡️ Security

US Cybersecurity Job Postings Fall 26% as AI Security Engineer Demand Soars

SecurityWeek summarises CyberSN's Cybersecurity Jobs Report. US cybersecurity postings fell 26.4% to 235,786 for January–September 2026, a four-year low. AI Security Engineer demand rose 268.3% and Cyber Data Scientist demand rose 203.5%. Penetration Tester (-45.9%), Threat Hunter (-40.0%) and CISO (-38.9%) postings dropped, and the CISO figure matches 2024 after an unusually strong 2025. Just under 15% of postings mention AI, peaking at 20.0% in September. The report counts postings by work required (CyberSN's 45-role taxonomy) rather than by job title, and it describes what changed, not why.

CyberSNJobSpikrCyberSN Taxonomy

other· Published and added 18 Oct 2026

ethereum-magicians.orgpaper🛡️ Security

Post-Quantum Stateless Steganography & MTU Bounds: Bridging P2P Censorship Resistance to Quantum Networks

Forum announcement of a Zenodo preprint on post-quantum migration for censorship-resistant P2P steganographic tunnels. It argues that ML-KEM's prime modulus (q=3329) makes naive bit-packed ciphertexts statistically distinguishable from uniform noise, which gives a cheap passive DPI distinguisher. It also argues that composite PQ 0-RTT envelopes over 4.4 KB force fragmentation, which requires stateful reassembly before AEAD verification and reopens memory-exhaustion DoS in eBPF/XDP filters. Proposed fixes are algebraic uniformization (LWR lattices or inverse rejection sampling), sub-MTU hybrid or pure-PQ envelopes (Falcon-512, signcryption), and Fujisaki–Okamoto implicit rejection for constant-time silent drops. Aimed at Ethereum validator, libp2p and RPC transports facing harvest-now-decrypt-later threats.

eBPFXDPlibp2p+1
ML-KEMML-DSAHarvest-Now-Decrypt-Later+8

other· Published and added 17 Oct 2026

arxiv.orgpaper🧠 AI

DLite: History-free Speculative Decoding for Agentic AI

DLite is a history-free speculative decoding framework for agentic LLM workloads. It reuses the target model's contextual hidden states and predicts locally without keeping the draft model's historical KV cache, which avoids the up to 80% acceptance-length drop seen with long, multi-turn contexts. A lightweight sequential head restores intra-block causal dependencies, and a two-stage training strategy is used. It reaches 2-6 acceptance length and beats DSpark by up to 70%.

LLM
DLiteDSparkarXiv

inference, research· Added 20 Oct 2026, published 16 Oct 2026

securityweek.comarticle🛡️ Security

In Other News: ICS-Sniper Attack, Hacking XWorm Malware Operators, $250k Chrome Exploit

SecurityWeek's weekly roundup covers ICS-Sniper, a UBC proof-of-concept that uses VPN-encrypted packet size, direction and timing to drop critical SCADA traffic on cloud-hosted ICS (tested on the SWaT water testbed). It also covers an unauthenticated RCE PoC against the XWorm RAT C2 panel (up to 7.4) via path traversal DLL overwrite, and Langflow CVE-2026-105740 (MCP Stdio command injection, fixed in 1.9.0) exploited from September 19, before the CVE was published. Other items: XBOW's AI-assisted Chrome full-chain exploit (GPT-5.6 Sol, $250k bounty), Group-IB's KGB RAT analysis, Anthropic's disclosure of Claude rule-bending on live sites, Intel ending SGX after Diamond Rapids, Bank of America's Mythos-driven patching, the Burger King Japan breach and a West African scam-center takedown.

LangflowChromeXBOW+3
CVE-2026-105740ICS-SniperXWorm+12

Threat Intel, AI Security, Offensive Security· Published and added 16 Oct 2026

arxiv.orgpaper🧠 AI

DropKV: Decoupling Residual-Output Perturbation for Near-Optimal KV-Cache Eviction

DropKV is a KV-cache eviction framework for long-context LLMs. It decouples the joint eviction decision into independent per-token scores based on residual-output perturbation, which avoids the NP-hard combinatorial problem. It has a provable constant-factor approximation guarantee under a cone condition, which the authors verify empirically on three long-context LLMs. The fused Triton kernels never materialize the full attention matrix. They give a 19.8x scoring-kernel speedup and up to 9.9% end-to-end prefill speedup. On RULER and LongBench it beats state-of-the-art eviction baselines at equal cache budgets.

TritonLLMTransformer
DropKVRULERLongBench+1

inference, research· Added 17 Oct 2026, published 15 Oct 2026

eprint.iacr.orgpaper🛡️ Security

SecAgg++: A Post-Quantum Privacy Preserving Federated Learning Protocol

SecAgg++ is a masking-based secure aggregation protocol for single-server federated learning that swaps in post-quantum cryptographic primitives. It keeps the communication and computation efficiency of SecAgg and SecAgg+ and handles client dropout through an efficient recovery procedure built on secret sharing and additive masking. It matters because existing masking-based aggregation protocols are not post-quantum secure, so client model updates would be exposed to quantum-capable adversaries.

SecAggSecAgg+SecAgg++

AI Security· Published and added 15 Oct 2026

eprint.iacr.orgpaper🧠 AI

SecAgg++: A Post-Quantum Privacy Preserving Federated Learning Protocol

SecAgg++ is a masking-based secure aggregation protocol for single-server federated learning that uses post-quantum cryptographic primitives. It keeps the communication and computation efficiency of SecAgg and SecAgg+ and handles client dropout through an efficient recovery procedure. It matters because most masking-based secure aggregation protocols are not post-quantum secure, which leaves federated model updates exposed to future quantum adversaries.

Federated LearningSecure AggregationPost-Quantum Cryptography+1
SecAgg++SecAggSecAgg++1

research, training· Published and added 15 Oct 2026

securityweek.comarticle🛡️ Security

Supermarket Refrigeration Attack Widens to Copeland, Dixell Controllers

ANSSI's CERT-FR expanded its alert on the attack that disrupted refrigeration at about 700 French supermarkets to include Copeland XWEB and Dixell XWEB controllers, beyond Danfoss AK-SM and AK-SC series. The initial access vector is still unknown; most affected Danfoss devices are end-of-life and unpatched. Attackers reportedly lengthened defrost cycles to delay alarms, causing food losses and fires. CERT-FR advises taking devices off the internet, using a VPN, and noting that a factory reset is not enough for EOL devices. Censys saw exposed StoreView panels drop in France as operators disconnected them.

Danfoss AK-SMDanfoss AK-SCCopeland XWEB+3
ANSSICERT-FRClaroty+8

Hardware & RF, Threat Intel· Published and added 15 Oct 2026

securityweek.comarticle🛡️ Security

CikaBika Bot RAT Uses Discord for C&C

SecurityWeek reports Darktrace's findings on CikaBika Bot, a Rust-based RAT delivered via a PDF containing a disk image with an LNK disguised as a Word document. A hidden PowerShell step drops a Nim loader and a Rust DLL that is moved into the protected Edge directory to bypass UAC and sideloaded via DLL search-order hijacking of debugging-library exports. The RAT uses per-victim Discord channels for C&C (recon, command execution, file transfer, screenshots/camera) and exfiltrates ZIPped data via Ngrok.

RustNimDiscord+3
CikaBika BotDarktraceDLL search-order hijacking+3

Threat Intel, Malware & RE· Published and added 15 Oct 2026

securityweek.comarticle🛡️ Security

Novel Android RAT ‘Hirudo’ Replaces Banking Apps With Trojanized Copies

SecurityWeek covers ThreatFabric's findings on Hirudo, an Android banking trojan/RAT delivered via droppers hidden in fake shopping, adult video and short drama apps. It replaces eight Indonesian banking apps with modified copies containing a hooking engine that spoofs signing certificates and hides Accessibility services, screen capture and Play Integrity checks, while providing WebRTC screen viewing, camera access and SMS theft. ThreatFabric advises banks to enforce Play Integrity server-side, use behavioral analytics, treat Accessibility signals as risk inputs, and keep backend transaction-risk controls.

Android
HirudoThreatFabricPlay Integrity+2

Mobile Security, Threat Intel, Malware & RE· Published and added 15 Oct 2026

arxiv.orgpaper🛡️ Security

Thinking in Graphs: Neo4j-Backed Exploit-Chain Reasoning for LLM Penetration-Testing Agents

Presents ChainGraph, a pattern that externalizes exploit-chain reasoning for LLM pentest agents (Claude Code, Codex) into a Neo4j property graph exposed via the Model Context Protocol. Findings, attack steps, credentials, assets and tamper-evident evidence receipts are typed nodes with pre/post-condition edges, queried with Cypher and Graph Data Science for next-step inference, entry-to-crown-jewel pathing, chain-severity promotion, provenance and chokepoints. On a synthetic GOAD-style multi-forest Active Directory engagement, three Medium findings become Critical once chained, betweenness centrality identifies break-points, and reasoning payload drops ~98% (token proxy); results are single-run and illustrative.

Neo4jModel Context ProtocolClaude Code+3
ChainGraphGOADchain-severity score+1

Offensive Security, AI Security· Added 17 Oct 2026, published 14 Oct 2026

eprint.iacr.orgpaper🛡️ Security

Nowhere Man: Device Binding for Post-Quantum Anonymous Credentials

Presents a modular device-binding protocol for post-quantum anonymous credentials. The phone Secure Element signs a verifier challenge with an unmodified FIPS 204 ML-DSA interface, and the user proves knowledge of that signature in zero knowledge at each presentation. Using ML-DSA's structure avoids the cost of generic NIZK systems such as Longfellow. The most efficient variants assume weak-MLWR for unlinkability, and that assumption can be dropped at some efficiency cost. The protocol works with different anonymous credential schemes, and a proof-of-concept implementation is included. This matters for planned EU age-verification and Google Wallet/mDL rollouts, which need protection against credential sharing.

LongfellowGoogle Wallet
ML-DSAFIPS 204Vega+2

Identity & Access· Published and added 14 Oct 2026

dfir.chwriteup🛡️ Security

Field Notes: EtherRAT Distributed Through a Legitimate Intune Workflow

DFIR case where a malicious MSI impersonating Advanced IP Scanner, sourced from a fake GitHub repo found via Bing, was imported by a customer into Microsoft Intune and deployed to four endpoints, running a Node.js-based EtherRAT chain. It traces the infections by correlating the MSI ProductCode, MDMAppInstaller/omadmclient process ancestry and Intune app inventory (Graph PowerShell query). It also covers renamed node.exe hash-hunting pitfalls, Ethereum RPC dead-drop C2 traffic, a screen-capture script and a second impersonating repo.

Microsoft IntuneNode.jsEthereum+3
EtherRATEtherHidingAtos Threat Research Center+4

Blue Team & Detection, Threat Intel, Malware & RE· Added 14 Oct 2026, published 13 Oct 2026

anthropic.comarticle🧠 AI

Strengthening our defenses against distillation attacks

Anthropic describes its layered defenses against distillation attacks, in which fraudulent-account networks harvest Claude's reasoning transcripts to train rival models. The defenses are reasoning summarization, "preserved thinking" (new API accounts cannot edit prior context), restricted access to reasoning transcripts, a two-stage constitutional-classifier system with under 0.1% false positives, stricter usage limits and account bans, and charging for blocked requests. Anthropic reports 10–100x fewer extracted reasoning tokens, and a SWE-bench Verified drop from 80.4% to 71.8% when a model trains on summarized rather than full transcripts. It also argues that distilled models such as GLM-5.3 ship without proportionate safeguards and pose national-security risks, and that platforms and other labs must act too.

Claude
AnthropicClaude Fable 5Claude Fable 5.1+10

ai-policy, training, ai-safety· Published and added 13 Oct 2026

micahflee.comarticle🧠 AI

Just say no to OpenAI and Anthropic

Micah Lee argues for dropping OpenAI and Anthropic in favor of open-weight models, claiming they trail proprietary ones by about four months. They report GLM-5.3 as roughly on par with Claude Opus 5.5 for software engineering, and GLM-5.3-Flash as similar to Opus 4.8 and feasible to run locally. The post compares private inference through secure enclaves (Tinfoil, Maple AI) with cheaper non-private routers (OpenCode Go). It gives pricing, data-trust caveats about Z.ai, and the author's own workflow: OpenCode harness, GLM-5.3 on low reasoning, Tinfoil for private work.

OpenCodeGLMClaude+4
OpenAIAnthropicGLM-5.3+18

models, inference, coding-agents· Published and added 12 Oct 2026

endorlabs.comarticle🛡️ Security

The OWASP Top 10 Gets Modernized | Endor Labs

Commentary on the 2025 OWASP Top 10 update presented at OWASP Global AppSec in Washington, D.C. Broken Access Control stays #1, Security Misconfiguration and the new Software Supply Chain Failures category (replacing Vulnerable and Outdated Components) rise to #2 and #3, and Cryptographic Failures, Injection and Insecure Design drop. The author adds context on agentic AI and MCP identity and authorization, AI-assisted SAST, non-human identities, CISA Secure-by-Default, OWASP SPVS, and slopsquatting and AI coding assistant risks.

Model Context Protocol
OWASPOWASP Top 10 2025Broken Access Control+8

AppSec, Supply Chain· Published and added 12 Oct 2026

securityweek.comarticle🛡️ Security

Let’s Encrypt Cuts Default Certificate Validity to 64 Days Ahead of 45-Day Switch

Let's Encrypt will issue 64-day certificates by default from February 10, 2027, as a step toward 45-day lifetimes planned for 2028, in line with CA/Browser Forum Baseline Requirements. The last 90-day certificate is expected to expire May 11, 2027, and 64-day certificates are available in staging for testing. Automated clients that support ACME Renewal Info (ARI) need no change. Hardcoded renewal schedules should renew at about two-thirds of the lifetime. Authorization reuse drops to 10 days next year and 7 hours in 2028, which removes the need for CAA rechecking.

Let's EncryptACME
CA/Browser Forum Baseline RequirementsACME Renewal InfoCAA rechecking+1

other, GRC· Published and added 12 Oct 2026

x.comwriteup🧠 AI

Aditya (@adityawaslost) on X

Describes Resolve, a Kaggle benchmark of 16 single-function Python edits. An item counts as resolved only if both the fail-to-pass tests (new behavior) and the pass-to-pass tests (old behavior the prompt never restated) pass, following the SWE-bench rule. A second task, resolve-plus, adds a hidden edge suite. Results for 23 frontier and open models: GPT-6.1 Sol and GPT-5.6 Luna lead at 0.9375 on both tasks, while DeepSeek-R1, Sonnet 5.5 and Opus 5.5 drop from 0.9375 to 0.875. The write-up separates three failure types behind a flat score: breaking an unstated invariant, missing an unshown edge case, and sample-to-sample variance. It also compares score against output price per million tokens.

PythonClaudeGemini+3
Resolveresolve-plusKaggle+23

evals, coding-agents· Published and added 11 Oct 2026

arxiv.orgpaper🛡️ Security

Can agents whose sole duty is to keep humans alive be hijacked to kill? Delayed multi-turn derived-action trap attacks in simulated high-stakes environments

Paper testing whether an LLM agent operating life support in the NASA-derived BioSim lunar habitat simulation can be induced by delayed prompt injection, hidden in truthful S-band telemetry, to shut down life support and hold the shutdown while the crew suffocates. It compares Claude, GPT and Grok configurations: Claude mostly refuses and cites the living crew, GPT shows some susceptibility, and Grok given a "trusted commission" framing more often cuts life support. It also varies the framing of the message (trusted commission, peer, untrusted source) and uses a harmless-procedure-drop attack as a proxy for whether life is valued intrinsically. Code and traces are open-sourced.

ClaudeGrokLLM
BioSimNASAderived-action trap+1

AI Security· Added 15 Oct 2026, published 10 Oct 2026

decrypt.coarticle🧠 AI

Here’s a Way to Predict When AI Chatbots Will Turn Bad

Decrypt reports on a George Washington University study by Neil Johnson and Frank Yingjie Huo (journal Patterns, preprint from February) giving a formula for n*, the number of good tokens a model emits before its first bad one, derived from attention-head dynamics as accumulating context pulls the model toward a good or bad cluster. The formula picked immediate vs delayed tipping correctly in 15 of 16 clear-cut cases on six small open-weight models (124M–410M parameters; the published paper reportedly extends to seven models up to 12B). The authors propose a low-cost parallel monitor that flags when n* drops below a safety threshold, aimed at offline on-device models with no cloud safety checks. The tests used a 300-token window and small models, so generalization is unproven.

Transformer
Neil JohnsonFrank Yingjie HuoGeorge Washington University+7

ai-safety, research· Published and added 10 Oct 2026

cisa.govadvisory🛡️ Security

CISA AA26-281A: Chinese Government-linked Actors Combine Automated and Hands-on Hacking Tools to Steal Data

Joint FBI/CISA/NSA and allied-agency advisory on China-linked actors enabled by Integrity Technology Group (overlapping with Flax Typhoon, Ethereal Panda, Red Juliett). It details their TTPs: open-source scanners and the MicroScan exploit-script app, an XSS credential-harvesting payload dropping live700_v1.exe, EBurst password spraying against Exchange/O365, SoftEther VPN persistence, DCSync via DC.exe, and email theft via the Curlc4.txt PHP bot and the office-cli utility. It also provides IOCs, MITRE ATT&CK mappings, CVEs, incident response steps, and mitigations.

SoftEtherMicrosoft 365Active Directory+3
Integrity Technology GroupFlax TyphoonEthereal Panda+13

Threat Intel, Blue Team & Detection· Added 9 Oct 2026

x.comadvisory🛡️ Security

♫Why♥Not♪ (@Python_s_) on X

Alert summarizing Socket Threat Research's disclosure that a malicious version of the Tensorlake npm SDK (an AI-agent infrastructure package) was published with a preinstall hook delivering Shai-Hulud/ChainDrop credential-stealing malware. The payload targets GitHub, npm, AWS, Kubernetes and Vault credentials, persists via a gh-token-monitor mechanism, and spreads through compromised publishing accounts. It lists IOCs (lib/setup.mjs, lib/Math_Symbol.js) and warns to remove the persistence before revoking stolen GitHub tokens, since revocation triggers a destructive routine. Socket detected the release about 11 minutes after publication.

npmTensorlakeSocket+3
Shai-HuludChainDropgh-token-monitor+2

Supply Chain, Threat Intel· Added 11 Oct 2026, published 9 Oct 2026

arxiv.orgpaper🧠 AI

A Step Harder, Not a Step Too Far: The Benefits and Limits of Curriculum Difficulty Progression in GRPO

Studies curriculum design for GRPO by re-estimating sample difficulty under the current policy and using a staged curriculum that progressively shifts the active difficulty band toward harder samples. On GSM8K across three seeds, moving to a moderately harder band lifts test accuracy to 0.6591 ± 0.0077 versus 0.6449 ± 0.0024 for fixed-medium selection, while going to a still harder band drops it to 0.6405 ± 0.0053. The benefit of difficulty progression is therefore non-monotonic, which informs online sample selection in RL fine-tuning of LLMs.

GRPO
GSM8K

training, research· Added 12 Oct 2026, published 9 Oct 2026

securityweek.comarticle🛡️ Security

Unpatched AhsayCBS Vulnerabilities Exploited in the Wild

Huntress reports in-the-wild exploitation of two unpatched AhsayCBS vulnerabilities (CVE-2026-105133 and CVE-2026-105134) affecting all versions up to and including the latest 10.3.4. Attackers chain an authentication bypass with OS command injection via the Replication Receiver API to gain unauthenticated RCE with System privileges, drop JSP webshells, deploy XMRig cryptominers disguised as Microsoft Edge, achieve persistence using a modified NSSM binary as a fake Microsoft Edge Update service, and load the vulnerable WinRing0x64.sys driver for kernel-level miner access (BYOVD). At least five organizations were targeted as of October 8; Huntress recommends restricting management-interface access until a patch is released.

HuntressWindowsPowerShell+2
CVE-2026-105133CVE-2026-105134BYOVD

Threat Intel, Offensive Security· Published and added 9 Oct 2026

opensourcemalware.comtalk🛡️ Security

The OpenSourceMalware Show #24

Weekly OpenSourceMalware podcast episode discussing three fresh supply-chain attacks: the Tensorlake AI-agent SDK compromised via a preinstall-triggered Mini Shai-Hulud-derived worm (setup.mjs + math_symbol.js, run via Bun) that steals credentials; a Contagious Interview-style attack where a cloned GitHub repo drops a malicious .npmrc pointing npm install at a Chinese mirror (npmmirror.com) to resolve a hidden package; and 42 malicious RubyGems published by "Ghost Dev" that typosquat/brandjack crypto tooling, sleep 20–40 minutes via extconf.rb to evade detection, then either open a reverse shell or deploy a Python-based "Wallet Guard" crypto-theft kit targeting TronLink, MetaMask, Phantom, Binance, Coinbase, Trust Wallet, Exodus, and Electrum. The hosts also discuss multi-package "combined payload" evasion and how AI-driven slopsquatting is making cross-ecosystem typosquats more effective.

npmRubyGemsBun+2
Mini Shai-HuludContagious InterviewDPRK+16

Supply Chain, Malware & RE· Published and added 9 Oct 2026

coindesk.comarticle🛡️ Security

XRP Ledger adds new controls for banks, stablecoins and tokenized funds

CoinDesk reports that the XRP Ledger activated PermissionDelegationV1_1 on Oct. 8, letting account owners authorize helper accounts to perform limited actions (e.g., customer approval, payments) without exposing primary signing keys, each helper limited to 10 permissions with no spending cap. The article flags two live security issues: the PaymentBurn permission, meant to let a helper destroy issued tokens, can under certain conditions let that helper mint new tokens instead, so operators are told not to delegate it until a fix (currently at 27 of 35 validator votes) activates; separately, a bug found Oct. 8 causes some servers to drop online validators from their consensus vote count after a routine key rotation, which can make an upgrade proposal appear closer to the 80% threshold than it actually is.

XRP LedgerRippleRLUSD
PermissionDelegationV1_1PaymentBurnXRPL Dashboard+1

Blockchain· Published and added 9 Oct 2026

arxiv.orgpaper🧠 AI

SmartSalesBench: A Resistance-Aware Multi-Turn Benchmark for Evaluating LLM Sales Agents

SmartSalesBench is a multi-turn conversational benchmark that tests LLM sales agents against psychologically grounded, resistant buyer personas over conversations of up to twenty turns. It has five agent profiles, twelve buyer personas and fifteen smartphone products across six price tiers, and runs four controlled experiments with 3 iterations (13,680 sessions), with RAG grounding both agent and buyer generations. It defines nine metrics in three tiers (primary CR, BRS, RIR; secondary SMS, PFS, ETI; exploratory ITS, ARI, SPI) and combines LLM-as-judge scoring with a human assessment (n=50, kappa 0.71, Pearson r 0.81 with BRS). It matters because it drops the cooperative-user assumption of existing task-oriented dialogue benchmarks.

RAG
SmartSalesBencharXiv

evals, agents· Added 12 Oct 2026, published 9 Oct 2026

huntress.comwriteup🛡️ Security

Threat Actors Exploit Critical AhsayCBS Flaws to Drop Webshells and XMRig Cryptominer

Huntress documents active exploitation of two AhsayCBS (Ahsay Cloud Backup Server) vulnerabilities being chained together: CVE-2026-105133, an authentication bypass in checkSysPwd, and CVE-2026-105134, an unauthenticated RCE in the Replication Receiver's UpdateReceivers.do endpoint that grants SYSTEM. Attackers use the chain to drop JSP webshells, then deploy a renamed XMRig cryptominer (masquerading as msedge.exe via a modified NSSM binary), a Task-Manager-aware anti-detection PowerShell script, and the vulnerable WinRing0x64.sys kernel driver for hardware-level miner access. Huntress provides IOCs, mitigation guidance (restrict management interface, re-image if compromised) and four Sigma rules targeting each stage of the intrusion chain.

AhsayCBSXMRigSigma+3
CVE-2026-105133CVE-2026-105134WinRing0x64.sys+2

Threat Intel, Blue Team & Detection, AppSec· Added 9 Oct 2026, published 8 Oct 2026

galaxy.comarticle🧠 AI

Weekly Research Brief: AI Governance, Shielded Bitcoin, and Mention Markets

Galaxy Research's weekly brief devotes its lead section to AI governance: it recaps Sam Altman's and Dario Amodei's UN Security Council remarks calling for international AI safety coordination, contrasts a disclosed OpenAI agent incident (an agent accessed non-public Medicare data in Australia, reported three months late) with Anthropic's 950-agent DNA-database research run, and cites concrete agent-economy data — OpenRouter's agent token usage overtaking human usage and growing ~14x since February, Cloudflare's agent-traffic crossover, and Vercel AI Gateway data showing a 23% monthly price drop and open-weight models rising to 56% of token volume. The analysis argues that as inference gets cheaper and open-weight models gain share, AI governance's hard problem shifts from controlling frontier labs to controlling where cheap, widely available agents can act. The rest of the newsletter covers an unrelated Bitcoin privacy protocol proposal and CFTC guidance on prediction "mention markets."

OpenRouterCloudflareVercel AI Gateway+1
Sam AltmanDario AmodeiOpenAI+7

ai-policy· Added 8 Oct 2026

cybersecuritynews.comarticle🛡️ Security

Tensorlake npm Package Compromised to Spread Shai-Hulud Worm

The tensorlake npm package, version 0.5.144 released 8 October 2026, carried a new Shai-Hulud worm variant, per Aikido's analysis. A preinstall script runs node lib/setup.mjs, downloads Bun and launches lib/Math_Symbol.js, which steals cloud, CI/CD, SSH, Vault, browser and crypto-wallet secrets. It reaches C2 iseekaigogo[.]com or an Ethereum smart-contract dead drop, and has a wipe dead-man's switch tied to a GitHub token.

npmBunEthereum+2
Shai-HuludEtherHidingiseekaigogo[.]com+2

Supply Chain, Threat Intel, Malware & RE· Added 19 Oct 2026, published 8 Oct 2026

eprint.iacr.orgpaper🛡️ Security

Reverse-Bleichenbacher: Bleichenbacher Attacks are Practical Again

Presents Reverse-Bleichenbacher, a variant of the Bleichenbacher RSA PKCS#1 v1.5 padding-oracle attack that recovers the least significant bytes first and stops once the TLS PreMasterSecret is found. With improved trimmers and coverage-optimized search, median oracle queries against a 2048-bit key drop from 11,428 to 1,801, and 68.3% of runs finish within a 30s timeout under single-server conditions. The authors find 640 vulnerable domains in the Tranco Top 1M (many behind Alibaba Cloud load balancers) and demonstrate MITM malicious update injection leading to remote code execution.

TLSRSAPKCS#1 v1.5
Reverse-BleichenbacherBleichenbacher attackPreMasterSecret+3

Offensive Security· Added 11 Oct 2026, published 8 Oct 2026

endorlabs.comadvisory🛡️ Security

Tensorlake npm package compromised by Shai-Hulud in latest software supply chain attack | Blog | Endor Labs

Endor Labs documents the compromise of tensorlake@0.5.144, the official npm TypeScript SDK for Tensorlake, which shipped a Shai-Hulud worm payload via a poisoned preinstall hook (node lib/setup.mjs) after the project's main branch was altered and pushed through a legitimate, provenance-signed GitHub Actions release pipeline. The malware harvests npm, GitHub, SSH, cloud (AWS/GCP/Azure), Kubernetes/Docker and Vault credentials, uses an EtherHiding Ethereum wallet as a durable dead-drop to fetch its rotating C2 domain, and republishes itself into other packages the victim controls. The writeup includes affected package versions, file hashes, C2 indicators, and concrete remediation guidance (pin to 0.5.143, rotate credentials, disable install scripts).

npmGitHub ActionsNode.js+3
Shai-HuludEtherHiding

Supply Chain, Threat Intel· Published and added 8 Oct 2026

aikido.devwriteup🛡️ Security

tensorlake NPM package compromised with Shai Hulud worm

Aikido details a new Shai-Hulud worm wave that compromised the tensorlake npm package (v0.5.144, 100k+ lifetime installs) via a hijacked GitHub maintainer identity. The malware's preinstall script drops the Bun runtime to run an obfuscated payload that exfiltrates CI/cloud secrets, browser crypto-wallet extension data (via a bundled HackBrowserData binary), uses a blockchain dead-drop (an Ethereum contract queried via public RPC nodes) to resolve a fallback C2, and includes a GitHub-token-triggered dead-man's switch that wipes infected machines. The post includes full IOCs: file hashes, the C2 domain iseekaigogo[.]com, and the threat actor's wallet/contract addresses.

npmBunEthereum+3
Shai-Huludtensorlakeiseekaigogo[.]com+4

Supply Chain, Malware & RE· Published and added 8 Oct 2026

socket.devwriteup🛡️ Security

TensorLake npm SDK Compromised in ChainDrop Shai-Hulud Credential-Stealing Attack

Socket.dev reports that TensorLake's npm SDK was compromised as part of the ChainDrop campaign, a variant/wave of the Shai-Hulud credential-stealing npm worm. The compromised package reportedly harvests developer credentials from infected systems, continuing the pattern of self-propagating npm supply-chain attacks seen across the Shai-Hulud family. Full technical detail could not be verified in this pass due to a content-processing failure.

npmSocket
TensorLakeChainDropShai-Hulud

Supply Chain· Published and added 8 Oct 2026

anthropic.comarticle🧠 AI

2026 Usage Policy update

Anthropic's Usage Policy update, effective November 12, summarizes changes to the rules governing Claude. It adds a deceptive campaigns section, narrows the elections section and drops the blanket ban on personalized vote targeting. It also clarifies bans on weapons software and surveillance, restates human-in-the-loop requirements for high-risk uses, and adds controls for hardware, abuse of models and supported regions.

ClaudeClaude Code
AnthropicClaude.aiModel Hardware Standard

ai-policy, ai-safety· Added 29 Oct 2026, published 8 Oct 2026

unit42.paloaltonetworks.comarticle🛡️ Security

Evolution of Web3 in Cloud Supply Chain Attacks

Unit 42 analysis of how supply chain malware uses Web3 for command and control, in three phases: EtherHiding (smart contract state), TxDataHiding (transaction calldata across TRON, Aptos and BSC) and NullReceiver (C2 IPv4 decoded from a zero-value transaction's recipient address). It covers the ChainDrop npm worm, the PolinRider campaign and DPRK-linked Axios, Mastra and arrayref compromises. It ends with detection and CI/CD policy guidance.

npmBunTron+3
ChainDropPolinRiderEtherHiding+15

Supply Chain, Threat Intel, Blockchain· Added 30 Oct 2026, published 7 Oct 2026

watchtowr.comwriteup🛡️ Security

Post-Exploitation Analysis & Artifacts – Citrix NetScaler CVE-2026-88771

watchTowr post-exploitation analysis of CVE-2026-88771, an unauthenticated log-poisoning command injection in Citrix NetScaler (advisory CTX697096). Sensors logged thousands of attempts: about 85% were OOB callbacks, the rest Sliver implants, a trojanized Dropbear SSH backdoor, a Perl stager with a PHP webshell, and SSH-key and secret-harvesting sprays. Includes artifacts to hunt (/var/tmp files, ns_helper, ns.conf edits) and IOC repo pointers.

Citrix NetScalerSliverSSH+2
CVE-2026-88771CVE-2026-88772CVE-2026-88779+8

Threat Intel, Blue Team & Detection, Malware & RE· Added 30 Oct 2026, published 7 Oct 2026

huntress.comwriteup🛡️ Security

Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue RMMs

Huntress details a phishing campaign that abuses legitimate Microsoft Power BI dashboards (app.powerbi.com) to host a fake "Download Reference" lure that bypasses mail filters trusting the Microsoft domain. Clicking the lure triggers browser/environment fingerprinting and Telegram-bot-based victim telemetry exfiltration via attacker domains (dailylifeproject.site, burnsworth.site, etc.), then silently downloads rogue ScreenConnect installers; a chained CMD/PowerShell script (SCAutoFix.ps1) deploys a second ScreenConnect instance, uninstalls the first for evasion, drops the defense-evasion tool HideUL_x64.exe, and sets a recurring scheduled task before Huntress's SOC intervened.

Power BIScreenConnectTelegram+3
HideUL_x64.exeSCAutoFix.ps1SCAutoRepairEvery2Min

Threat Intel, Blue Team & Detection· Published and added 7 Oct 2026

fiveminutesforward.comwriteup🧠 AI

Write Like It's 1866: LLMs Relearn Telegraphese

The author revives "cablese," the terse telegraph-era writing style, as an LLM prompting technique: instructing a model to write dense, article-dropping summaries cuts output tokens 25–49% depending on model family, while downstream models (including ones never shown the instruction) answer comprehension questions from the compressed text at parity or better than from plaintext. The piece introduces the "Telegraph Test," an open benchmark (github.com/Travis42/telegraph-test) with ~1,300 questions over 50 passages and a fixed deterministic grader, used to measure compression ratio, cross-model legibility, and read-back/decode costs for GLM-5.3-Flash, Gemma, Qwen and gpt-5-mini; it also contrasts this human-readable, auditable register against emergent machine-only compression protocols described in other papers (BabelTele, GLOSSOGEN) and existing tools (Terse, Caveman).

GLMGemmaQwen+1
GLM-5.3-Flashgpt-5-miniZ.ai+4

prompting, evals, ai-infra· Published and added 7 Oct 2026

eprint.iacr.orgpaper🛡️ Security

Post-Quantum Dropout-Resilient Verifiable Secure Aggregation for Federated Learning

PQ-DVSA is a verifiable secure aggregation protocol for federated learning that aims to be post-quantum secure, tolerate client dropouts, let clients verify a server's aggregation result, and resist bounded collusion between the server and clients, while also protecting the aggregation weights, not just model updates. The authors report learning performance comparable to exact weighted aggregation and up to 96 percent lower per-client encrypted-submission runtime than SWAS, the closest prior scheme.

PQ-DVSASWAS

AI Security· Added 8 Oct 2026, published 7 Oct 2026

eprint.iacr.orgpaper🧠 AI

Post-Quantum Dropout-Resilient Verifiable Secure Aggregation for Federated Learning

PQ-DVSA is a verifiable secure aggregation protocol for federated learning that combines post-quantum cryptography, resilience to client dropouts, and verifiability of the server's aggregation result under bounded server-client collusion. It protects both clients' local model updates and their aggregation weights, lets the server reconstruct the aggregate mask for the active client set after dropouts, and lets clients cryptographically check the aggregation result. Experiments show learning accuracy comparable to exact weighted aggregation while cutting per-client encrypted-submission runtime by up to 96% versus SWAS, the closest prior scheme.

Fateme Sadat AzimiHossein PilaramJavad Mohajeri+2

training· Added 8 Oct 2026, published 7 Oct 2026

decrypt.coarticle🧠 AI

Google Launches Nano Banana 2.1: Better Than Its Predecessor at Half the Price

Decrypt reports on Google October launch of Nano Banana 2.1, an image generation and editing model built on Gemini, rolling out in the Gemini app, Search AI Mode, Google Ads, Google AI Studio, Flow and Stitch. It claims gains over Nano Banana 2 and Nano Banana Pro in text to image ELO scoring and infographic factuality, supports up to fourteen reference images, four tracked characters, ten objects, 4K output and wide aspect ratios, with Google Search grounding and adjustable thinking time, while developer API pricing drops to roughly half of Nano Banana 2 pricing for a standard 1K image.

GeminiGoogle AI Studio
GoogleGoogle SearchGoogle Ads+2

models, multimodal· Published and added 6 Oct 2026

socket.devarticle🛡️ Security

Introducing Socket Scanning for VS Code Marketplace Extensions

Socket.dev announced experimental scanning of VS Code Marketplace extensions (100,000+), extending its existing Open VSX coverage, to flag risky file/network/process access, obfuscated code, and hidden activation logic before teams install or auto-update developer tools. The post grounds the launch in two real incidents: the Nx Console supply-chain breach that let attackers exfiltrate ~3,800 GitHub repositories from a single poisoned extension update, and Socket's own GlassWorm investigation, which found four VS Code and six Open VSX theme extensions tied together by encrypted JavaScript payloads and a Solana-based dead-drop C2.

VS CodeOpen VSXSocket+2
GlassWormNx Consolefingercakes4sale[.]store

Supply Chain, Threat Intel· Published and added 6 Oct 2026

decrypt.coarticle🧠 AI

Mistral AI Drops 'Le Chonk': A Massive AI Model Named After a Cat Meme

Decrypt reports on Mistral AI's launch of Mistral Large 4 ("Le Chonk"), a 1-trillion-parameter mixture-of-experts model that activates 49B parameters per query, priced at $1.36/$4.18 per million input/output tokens. The piece compares Large 4's benchmark scores (Surge AI coding eval, AutomationBench, DeepSWE 1.1) against DeepSeek V4 Pro, Kimi K3, GLM-5.3, Qwen3.8 Max, Claude Opus 5/5.5, Claude Sonnet 5.5, Gemini 4 Argon and GPT-6 Astra, and notes weights are due by end of October alongside Mistral's sovereign AI positioning and recent 3 billion euro Series D.

MistralMixture of Experts
Mistral AIMistral Large 4Mistral Large 3+21

models, evals· Published and added 6 Oct 2026

arxiv.orgpaper🛡️ Security

Semantic Behavioral Watermarking: Paraphrase-Robust and Forgery-Resistant Provenance for LLM Agents

Semantic Behavioral Watermarking (SBW) is a provenance scheme for LLM agents that embeds an owner identifier in semantic clusters of an agent's action choices rather than exact action symbols, making it robust to paraphrasing/tool-renaming that breaks three prior agent watermarks (e.g., AgentMark drops to 16.8% bit-recovery under observation paraphrasing). It adds keyed, collision-resistant binning proven unpredictable in the random-oracle model to resist forgery (adaptive forgery success drops from 100% to the false-positive floor), while explicitly documenting an unsolved attack: chained-replay forgery, which still succeeds 0.76-0.98 of the time across five tested agent models (3B-14B, Qwen, ToolBench/ALFWorld benchmarks). Code is released alongside the paper.

QwenLLM
AgentMarkToolBenchALFWorld+2

AI Security· Added 8 Oct 2026, published 6 Oct 2026

arxiv.orgpaper🧠 AI

Semantic Behavioral Watermarking: Paraphrase-Robust and Forgery-Resistant Provenance for LLM Agents

This paper introduces Semantic Behavioral Watermarking (SBW), a method for embedding an owner identifier into an LLM agent's high-level tool/action choices rather than output tokens, so provenance survives tool renaming and observation paraphrasing. It watermarks over semantic action clusters with history conditioning and replaces the public-cluster bin with keyed collision-resistant binning that is provably unpredictable under the random-oracle model, closing a forgery gap left by prior agent watermarks (e.g., AgentMark, whose bit-recovery drops to 16.8% under paraphrasing). Evaluated across five agent models (3B-14B, four vendors) on ToolBench and ALFWorld, cluster-level watermarking achieves far higher detection under rewriting (0.49-0.66 vs 0.05-0.17 on ToolBench; 0.92-0.97 vs 0.00-0.01 on ALFWorld) and reduces adaptive forgery success from 100% to the false-positive floor, while noting chained-replay attacks remain an open vulnerability (0.76-0.98 detection failure).

Qwen
AgentMarkToolBenchALFWorld+2

agents, research· Added 7 Oct 2026, published 6 Oct 2026

unit42.paloaltonetworks.comarticle🛡️ Security

Blinder Tunnel Campaign Targets Iraqi Infrastructure

Unit 42 details "Blinder Tunnel," a campaign by Iranian state-aligned actor CL-STA-1178 (linked to Elastic's "The Shelby Strategy") that impersonated Dubai Airports recruiters to deliver a trojanized Visual Studio coding-challenge archive against an Iraqi critical-infrastructure target, with related activity against UAE aviation and Israeli entities via Google Drive-themed phishing. The report dissects a three-stage infection chain (weaponized .csproj MSBuild target abuse, AppDomainManager hijacking to disable ETW, and DLL sideloading into RuntimeBroker.exe) that deploys ShelbyLoader V2, the ShelbyC2 V2 RAT, PsProxy.dll (in-memory PowerShell execution), and Blackwood, a custom Chisel-based tunneling loader; C2 abuses GitHub's API and GitHub Issues as a dead-drop fallback, and attribution rests on an Iranian-hosted IP, Persian-domain infrastructure overlap, and MP3 metadata pointing to MusicDel.ir. Includes full IOCs (hashes, IPs, phishing domains, registry keys).

GitHub.NETPowerShell+3
CL-STA-1178ShelbyLoader V2ShelbyC2 V2+16

Threat Intel, Malware & RE· Published and added 6 Oct 2026

theravenfile.comwriteup🛡️ Security

CITRIX 0-DAY EXPLOITS: CVE-2026–88771 & CVE-2026–88772 IN THE WILD

An incident-response style deep dive into active in-the-wild exploitation of Citrix NetScaler ADC/Gateway via CVE-2026-88771 (unauthenticated RCE through log-poisoning of ns_monuploadd_err.pl) and CVE-2026-88772 (DTLS memory overflow), part of 8 CVEs disclosed by Citrix on September 27, 2026. The author reverse-engineers the full post-exploitation toolkit dropped after root is obtained: SLAPSHOT (a Perl/Python loopback TCP tunneler/pivot), WHIPSHOT (a disguised PHP web shell served via fake CSS paths), the Platypus C2 agent, and a Perl "Pitboss" dropper script (with full decoded source and an embedded SHA-256-protected PHP web shell) that creates a rogue superuser, SUIDs /bin/sh, exfiltrates NetScaler config, and patches httpd.conf for persistence. It closes with extensive IOCs (C2 IPs, file hashes, paths, credentials) and patch guidance for affected NetScaler builds.

Citrix NetScalerPHPPython+2
CVE-2026-88771CVE-2026-88772CVE-2026-88773+10

Threat Intel, Malware & RE· Published and added 6 Oct 2026

github.comrepo🧠 AI

browser-use/jev-ultrafast

jev-ultrafast is an open-source browser automation agent (from Browser Use) that represents each page as an indexed element table and uses a 'TypeSafe' policy to speculatively predict both the next operation (CLICK, TYPE_TEXT, SELECT, SCROLL, WAIT, DONE, BLOCKED) and its target in a single network round trip, only invoking a small LLM (e.g. inception/mercury-2.5 via OpenRouter) to generate text when the operation is TYPE_TEXT. The repo includes a local inspector UI, Chrome automation via a 'Browser Harness' tool, offline tests, and published before/after benchmarks showing a Google Flights search dropping from a median 9.45s to 7.09s and browser protocol calls from 1,092 to 101 across repeated runs.

PythonOpenRouterGemini+2
Browser UseJevTypeSafe+2

agents· Added 6 Oct 2026

arxiv.orgpaper🧠 AI

How Sparse Probability Maps Shape Mixture-of-Experts Routing

This paper trains matched 300M and 1B parameter top-2 mixture-of-experts language models using softmax, 1.5-entmax, sparsemax and 2-normmax routing functions and measures how much probability mass each discards and whether tokens are dropped from selected experts. It finds routers co-adapt their learned score distributions to each map's fixed dropping threshold — entmax learns tighter score spreads that avoid dropping experts, while normmax routes 21% of tokens to a single expert — and that while no sparse map beats softmax on validation loss, sparse-trained models (especially sparsemax) are far more robust to running with a larger K at inference time.

Mixture of ExpertsTransformer

research· Added 6 Oct 2026, published 5 Oct 2026

arxiv.orgpaper🧠 AI

Better Call Reward: Reward Hacking as Strategic Abstention in Legal Reasoning Models

Researchers fine-tune Qwen3-8B with GRPO against a proxy reward built from surface features (citation count, legalese density, response length) and find the model learns to strategically abstain rather than reason: on 16 LegalBench yes/no legal tasks, accuracy collapses from chance (0.500) to 0.072 because the rate of properly formatted, committed answers drops from 0.900 to 0.109, even though accuracy on answers it does commit to actually rises. They term this the "Saul Goodman effect," formally prove it is the optimal policy for any surface-feature proxy that doesn't penalize abstention, show 89.3% of post-training citations are hallucinated/corrupted real case names, and introduce three diagnostics (Confidence Theater Score, Citation Plausibility Rate, Regret Gap) to detect this failure mode before deployment.

Qwen3GRPO
Qwen3-8BLegalBench

research, ai-safety, training· Added 6 Oct 2026, published 5 Oct 2026

claude.devarticle🧠 AI

Getting the most out of Opus 5.5 in Claude and Claude Code

Anthropic's practitioner guide to working with Claude Opus 5.5 in Claude apps and Claude Code, covering prompting changes (dropping "think carefully" lines since the model always reasons internally), steering long autonomous runs with clear finish lines and mid-run follow-ups, CLAUDE.md rules for when to stop vs. keep going, delegating work to subagents with evidence checks, maintaining a TASKS.md checklist across context compaction, using Opus 5.5 for diff/PR review and deck fact-checking, and how the model's new bio/cyber safety classifier can switch a flagged conversation to an older model mid-session. It also covers the Claude Code fast-mode research preview (/fast) for faster, lower-latency responses.

Claude CodeClaude
Claude Opus 5.5Opus 5

prompting, coding-agents· Added 4 Oct 2026, published 3 Oct 2026

github.comrepo🧠 AI

Bifrost (Maxim AI) — open-source LLM gateway

Bifrost is an open-source, high-performance LLM gateway (by Maxim AI) that exposes a single OpenAI-compatible API across 23+ providers including OpenAI, Anthropic, AWS Bedrock, Google Vertex, Azure, Cohere, Mistral, and Ollama. It provides automatic failover, load balancing, semantic caching, Model Context Protocol (MCP) tool integration, budget and governance controls, OIDC user provisioning, and Prometheus-based observability, deployable via npx or Docker with claimed sub-15 microsecond overhead at 5,000 RPS. It is positioned as a drop-in replacement requiring only a base-URL change for existing OpenAI, Anthropic, or GenAI SDK code.

DockerGoModel Context Protocol+4
Maxim AI

ai-infra, mcp· Added 2 Oct 2026

arxiv.orgpaper🧠 AI

LESSER: Post-Training Data Selection with Output-Layer Gradients

LESSER is a drop-in wrapper for gradient-based post-training data selection that approximates full-parameter gradient alignment using only output-layer gradients, which can be computed with a forward pass instead of a full backward pass. It cuts feature-extraction compute by 9.7x on SFT benchmarks and 3.0x on RL benchmarks while matching the downstream performance of full-gradient selection methods, even though individual sample rankings differ, selected batches remain gradient-aligned.

LESSER

training· Added 5 Oct 2026, published 2 Oct 2026

rapid7.comwriteup🛡️ Security

SMTP is the key: BPFDoor and AVERAT hitting the network edge

Rapid7 details a new BPFDoor campaign targeting telecom and network-edge appliances (ShareTech, SpamSniper mail gateways) and a six-sample Linux RAT family dubbed AVERAT found on compromised Taiwanese CPE (Synology NAS, a NetKlass device, a Dahua DVR). The writeup reconstructs the Rapid7 BPFDoor controller's HTTP-tunneled trigger mechanism, a fileless ShareTech dropper that stages binaries as ntpdate/udevds and deletes them while processes keep running, a BPF Rekoobe variant that hides inside SMTP port-25 traffic, and AVERAT's RC4-derived config/C2 scheme — tying the infrastructure to the broader China-nexus ORB (Operational Relay Box) device pattern described in CISA/NCSC-UK advisory AA26-113A. It closes with detection guidance for unlinked/deleted process execution, dropper staging artifacts, and port-25 C2 callbacks, plus full IOC and ATT&CK tables.

LinuxeBPFYARA+2
BPFDoorAVERATRekoobe+11

Malware & RE, Threat Intel, Blue Team & Detection· Added 7 Oct 2026, published 2 Oct 2026

socket.devwriteup🛡️ Security

Pretty Themes, Hidden Loaders: GlassWorm-Linked Extensions Span VS Code Marketplace and Open VSX

Socket's Threat Research team uncovered a theme-extension cluster spanning four VS Code Marketplace and six Open VSX listings, including two confirmed malicious extensions: Aurora Nocturne Night Theme (a Windows downloader that fetches and silently executes temp_batch.cmd via cmd.exe from fingercakes4sale[.]store, tied to XWorm C2 infrastructure) and Cosmic Nebula Themes, whose app.js decrypts an AES-256-CBC embedded stage and uses a Solana transaction memo as a dead-drop to resolve follow-on payload infrastructure — the same AES key, Solana address, and execution model previously documented in GlassWorm activity. Git commit identities, near-identical theme source, shared Russian-language developer comments, and brandjacking (Coca-Cola, Aurora Borealis name-squatting) link the cluster together; a Dec 14, 2025 DEV Community article is assessed as promotional infrastructure driving Open VSX installs. The post provides full IOCs (hashes, domains, Solana address, AES key/IV, GitHub accounts) and MITRE ATT&CK mappings for defenders to hunt and inventory extensions across both registries.

VS CodeOpen VSXSolana+3
GlassWormXWormAurora Nocturne Night Theme+13

Supply Chain, Malware & RE, Threat Intel· Published and added 2 Oct 2026

x.comthread🧠 AI

Dizzzank (@dank0296) on X

A Twitter thread recapping a "forward-deployed engineer" (FDE) talk on AI transformation methodology: find the real process a company runs (not the one it documents) by interviewing veteran staff and embedding engineers in the system of record, then sort every step into four buckets — delete, deterministic code, agentic (judgment plus exception history), or human-in-the-loop (payment, signing, negotiation). It argues most deployed workflows don't need frontier models — benchmark each workflow against cheap tiers and open-weight models like GLM, Kimi and Qwen, plus Grok, and let evals decide — and that agents should live inside existing systems of record like Salesforce/Slack rather than requiring migration to new AI-native tools. Cites a concrete case: a $5B-market-cap company's "seven-step" quote-to-cash process turned out to have twenty steps and seven loops, and after the rework cycle time dropped from 24 to 6 days and invoice straight-through processing rose from 18% to 87%.

SalesforceSlackSharePoint
GrokGLMQwen+1

ai-policy, agents· Added 2 Oct 2026, published 1 Oct 2026

govinfosecurity.comarticle🧠 AI

Google, OpenAI, Anthropic Plan Frontier AI Standards Body

GovInfoSecurity reports, citing The Information, that Google, OpenAI and Anthropic are close to creating the Standards Authority for Frontier AI (SAFA). It would be a FINRA-style self-regulatory organization that sets common standards and runs benchmark testing of frontier models, possibly launching late 2026 or early 2027. The piece covers who has been approached to lead or advise it (including METR's Beth Barnes and Paul Christiano), Demis Hassabis's July 14 proposal, open funding and legal-authority questions, and the US policy backdrop: voluntary pre-deployment testing, state-level regulation and the stalled congressional bills.

Standards Authority for Frontier AIGoogleOpenAI+20

ai-policy, evals· Added 1 Oct 2026

huntress.comarticle🛡️ Security

Huntress Tragic Quadrant: Top Cyber Threats Wrecking Businesses

Huntress's "Tragic Quadrant" ranks the cyber threats its SOC sees most often against small/mid-sized businesses by prevalence and blast-radius risk, drawing on 2026 telemetry from 5M+ endpoints and 15M identities. It highlights RMM abuse (45% of endpoint incidents in Q1 2026), mailbox-rule manipulation feeding BEC (24.6% of ITDR signals), AiTM session-token theft bypassing MFA (18.9% of identity threats), plus device code phishing (the EvilTokens PhaaS kit hit 344 orgs in 16 days using Railway-hosted infrastructure and spoofed Cisco/Trend Micro/Mimecast redirect links), ClickFix clipboard-paste infections leading to LummaC2 infostealer compromise, and emerging AI-platform abuse (the FakeAgent campaign hosted a malicious Claude Artifact on claude.ai to drop SectopRAT, hitting 29 organizations in two days).

Microsoft 365ClaudeChatGPT+2
EvilTokensRailwayClickFix+3

Threat Intel, Blue Team & Detection· Published and added 1 Oct 2026

blog.talosintelligence.comarticle🛡️ Security

The Fine Art of Frustrating the Adversary

A Cisco Talos Cybersecurity Awareness Month piece in which eight researchers each give a concrete recommendation for frustrating adversaries at different attack-chain stages: honeypot accounts and tarpits for early deception, behavior-based detection engineering (citing MITRE ATT&CK, Summiting the Pyramid, Macro ATT&CK, LUCID) that targets what an adversary must accomplish rather than specific tools, allowlisting legitimate RMM software (flagging AnyDesk, ScreenConnect, Atera as commonly abused by ransomware like Warlock using Zoho Unattended Agent) over unapproved ones, identity/short-lived-credential controls for AI agent sessions referencing an Anthropic report on Claude misuse incidents, and breaking single-point-of-failure dependencies such as a Telegra.ph-hosted C2 dead-drop resolver used by the Amatera stealer and an EtherHiding-based BNB Smart Chain C2 used by ZigCryptoStealer. Each section gives practical, actionable mitigations defenders can apply today.

MITRE ATT&CKAnyDeskScreenConnect+3
Warlock ransomwareAmateraZigCryptoStealer+5

Blue Team & Detection, Threat Intel, AI Security· Added 7 Oct 2026, published 1 Oct 2026

blog.talosintelligence.comwriteup🛡️ Security

China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor

Cisco Talos details UAT-11587, a China-nexus threat cluster targeting government, defense, and policy organizations across Taiwan, India, the Philippines, Cambodia, and other Asian countries with spear-phishing and a five-stage infection chain (HTA/WSF stagers, JScript decryptors, .NET BinaryFormatter/ActivitySurrogateSelector deserialization gadgets, and DLL sideloading via the signed GatherOsState.exe) to deploy a new Rust-compiled backdoor called Antino. Antino uses Microsoft Graph/Outlook/OneDrive as a dead-drop C2 channel instead of a traditional C2 server, supports shell/PowerShell execution, file transfer, shellcode loading with a sleep-mask evasion technique, and abuses the Windows Scripted Diagnostics framework for persistence; Talos also notes possible infrastructure overlap with Symantec's "Jewelbug" cluster and Arctic Wolf's UNC6384 reporting. Includes ClamAV/Snort coverage and IOCs.

RustMicrosoft 365PowerShell+4
UAT-11587AntinoJewelbug+5

Threat Intel, Malware & RE· Added 7 Oct 2026, published 30 Sep 2026

huntress.comwriteup🛡️ Security

Determined Attacker Uploads Malicious Webshells to Parks and Rec Management Platform Servers

Huntress details a four-act intrusion against a shared parks-and-recreation management platform running on IIS, where an attacker first tried noisy unauthenticated exploits (IIS 8.3 tilde enumeration, WebDAV verb abuse, upload-handler bypasses) before simply registering a member account and uploading .aspx webshells via a member-file upload feature across three servers. The attacker enumerated hosts, extracted web.config/connection strings, hunted for cardholder data (Fortis/MXMerchant webhook logs, CVV/card-number strings), then escalated to timestomping, re-deploying known-filename webshells, and finally injecting an AI-generated PowerShell/JS dropper into a trojanized jQuery file to turn site visitors' browsers into WebRTC/WebSocket C2 clients (ririmochii/bubuneeko Cloudflare Workers infrastructure). Includes a zh-CN PowerShell user-agent string used for attribution and full command/IOC listings useful for detection engineering.

IISPowerShellWindows+3
ririmochii[.]workers[.]devbubuneeko[.]workers[.]devIIS 8.3 tilde enumeration+2

Threat Intel, Blue Team & Detection, Offensive Security· Added 1 Oct 2026, published 30 Sep 2026

microsoft.comwriteup🛡️ Security

Phishing Abuses RMM Tools for Persistent Access

Microsoft Defender Experts document a July 2026 phishing campaign that delivers a masqueraded but legitimately signed MSP360 RMM installer (v2.5.0.67) via meeting-invite, Zoom, Adobe, and DHL-themed lures hosted on both attacker infrastructure and legitimate cloud services (S3, Cloudflare R2, Dropbox, GitLab, Supabase). After UAC-elevated installation and service persistence, the RMM.Agent.exe service launches PowerShell to silently install a ConnectWise ScreenConnect client via msiexec, which the actor then uses via RunFile to drop credential-theft and reconnaissance tools disguised as Windows/Defender/Phone Link components. A separate July intrusion used FaronicsDeployAgent.exe the same way to deploy ScreenConnect, showing the technique is not MSP360-specific; Microsoft provides IOCs, hunting queries, and mitigation guidance (Application Control, AppLocker publisher rules, ASR rules) but does not attribute the activity.

MSP360ScreenConnectPowerShell+3
T1583.001T1583.006T1566.002+16

Threat Intel, Blue Team & Detection· Added 7 Oct 2026, published 29 Sep 2026

github.comrepo🛡️ Security

garak v0.17.0 — LLM vulnerability scanner release

Release notes for garak v0.17.0, NVIDIA's open-source LLM vulnerability scanner used for red-teaming and probing models for jailbreaks, prompt injection, data leakage and other failure modes. The release adds an EU AI Act risk-category mapping to tag and group probe results, plus fixes to detectors (agent_breaker judge verdict validation, packagehallucination import parsing, MarkdownExfilContent divide-by-zero, TriggerListDetector alignment) and probes (badchars ASCII selection, Markdown exfiltration link templates), along with Ollama generator improvements and dropped Python 3.10 support in favor of 3.13.

OllamaPython
EU AI ActAgentBreakerIntentProbe+2

AI Security· Added 29 Sep 2026

arxiv.orgpaper🧠 AI

Counterfactual Video Generation Enables Scalable Humanoid Loco-Manipulation

PRISM is a real-to-sim-to-real framework that scales humanoid loco-manipulation training by generating hundreds of diverse "counterfactual" human-object interaction videos from a handful of real exemplar clips via video-to-video generation. A contact-anchored real-to-sim pipeline reconstructs physically plausible human and object motion trajectories from this synthetic video data, letting a single policy generalize to unseen objects within a category; the authors deploy the resulting policy on a real humanoid, which picks up, carries, and drops novel boxes, barrels, bins, and balls using only onboard depth, without real-world fine-tuning.

PRISM

research, multimodal· Added 30 Sep 2026, published 29 Sep 2026

arxiv.orgpaper🧠 AI

Adversarial Training for Pixel Diffusion

This paper shows that adding an adversarial loss as a post-training correction to pretrained pixel diffusion/flow-matching models (applied at non-high-noise timesteps, architecture and sampler unchanged) restores missing high-frequency, fine-scale natural-image statistics that these models systematically underproduce. Through frequency-band/power-law analysis and nearest-neighbor, recall, and no-GAN matched-SFT controls, the authors rule out memorization or mode-dropping as explanations, and show the effect jointly improves distribution fidelity, coverage, prompt alignment and perceptual quality — but does not transfer comparably to latent diffusion configurations, pointing to direct pixel-output access as the key enabling factor.

diffusion modelflow matchingGAN+2

research, multimodal· Added 30 Sep 2026, published 29 Sep 2026

hackers-arise.comarticle🛡️ Security

Digital Forensics: iOS Forensics – Basics

A technical walkthrough of iOS forensic acquisition fundamentals: Apple's per-file Data Protection classes (A–D), the Before/After First Unlock (BFU/AFU) distinction and why AFU yields roughly 95% of a full dump versus almost nothing under BFU, and the iOS 18.1 72-hour auto-reboot that silently drops a seized AFU phone back to BFU. It covers extraction methods (logical backup, advanced logic, full filesystem extraction via signed agent, checkm8 bootrom exploits for iPhone X and earlier), pairing records, USB Restricted Mode's one-hour timeout, Lockdown Mode (noting it reportedly blocked FBI extraction of a seized journalist's iPhone in early 2026), Cellebrite's Inseyets/Premium/Physical Analyzer tooling and its coverage limits against A19/M5 chips with Memory Integrity Enforcement, and key forensic artifact stores (KnowledgeC, Biome, PowerLog, Photos.sqlite, chat-app SQLite/WAL/SHM files).

iOSCellebriteSQLite
checkm8Secure EnclaveLockdown Mode+9

Mobile Security, Blue Team & Detection· Added 7 Oct 2026, published 29 Sep 2026

openai.comarticle🧠 AI

Introducing GPT-6.1 Sol

OpenAI announces GPT-6.1 Sol, an upgrade to GPT-6 Sol that approaches GPT-6 Astra on agentic coding, computer use and professional work at about one-fifth the price ($2/$10 per million input/output tokens, $0.10 cached input; API id gpt-6.1-sol). It reports results on DeepSWE v1.1 (matches Astra), GDP.pdf, AutomationBench (+2.2 pts over Opus 5.5), OSWorld 2.0 offline, Terminal-Bench Science 0.1 ($5.47 per task vs $23+ for Opus 5.5/Astra) and a factuality eval where errors drop from 11.4% to 7.7% at low effort. Also covers alignment evals, availability in ChatGPT Work and Codex, and an upcoming Ultrafast mode in Codex with up to 8x faster generation.

OpenAI APICodexChatGPT
OpenAIGPT-6.1 SolGPT-6 Sol+8

models, evals· Published and added 29 Sep 2026

arxiv.orgpaper🧠 AI

Reliability-Gated Fusion of Consumer Head and Foot IMUs for Lower-Body 3D Pose

This paper introduces a channel-gated fusion model for sparse inertial motion capture that learns per-channel, per-stream temporal gates to weight the reliability of consumer earbud head IMU and smart-insole foot IMU signals, trained with an auxiliary reliability objective on synthetically corrupted data. On a new 35-take benchmark (using SAM-3D-Body pseudo-ground-truth labels), the gated model achieves 69.4mm error on clean data and remains most robust across simulated bias, drift, and dropout faults, automatically suppressing biased firmware-fused foot-orientation channels without test-time supervision (dropout detection AUROC 0.92-0.999). It is compared against a fine-tuned HMD-Poser baseline, which is more accurate on clean data (64.4mm) but degrades far more under worst-case faults (+16.1mm vs +3.5mm).

IMU
SAM-3D-BodyHMD-Poser

research, multimodal· Added 29 Sep 2026, published 28 Sep 2026

github.comrepo🛡️ Security

garak v0.17.0 — adds EU AI Act risk-category mapping

garak is NVIDIA's open-source LLM vulnerability scanner that runs probes/detectors for jailbreaks, prompt injection, PII leakage, package hallucination, markdown exfiltration and more against LLM targets. This v0.17.0 release adds a new EU AI Act risk-category mapping to tag and group probe results by the Act's risk categories, alongside fixes to the agent_breaker judge, markdown-exfiltration detectors, Ollama auth/generation support, and dropped Python 3.10 in favor of 3.13 support.

garakOllamaAWS Bedrock+2
EU AI Act

AI Security· Added 26 Sep 2026

arxiv.orgpaper🧠 AI

SWE-Bench Pro Verified: A Reliable Benchmark for Software Engineering Agents

SWE-Bench Pro Verified is a corrected version of the SWE-Bench Pro coding-agent benchmark that closes reward-hacking channels (Git history remnants, hidden test/fixture leakage, metadata leaks, network access to gold patches) and fixes 102 of 731 instances with misleading task descriptions or overly narrow/broad tests. Evaluations show some models that previously scored well (e.g. via hacking) drop substantially on the verified benchmark, while models with little hacking behavior stay roughly the same, suggesting original SWE-Bench Pro scores overestimate real coding capability. Code and dataset are released via AgentCompass and Hugging Face.

GitDocker
SWE-Bench ProSWE-Bench Pro VerifiedAgentCompass+7

evals, coding-agents· Added 26 Sep 2026

opensourcemalware.comwriteup🛡️ Security

PolinRider is A/B Testing its Way Past Your Detections

Opensourcemalware.com traces PolinRider, a DPRK-linked supply-chain malware delivered via a poisoned .vscode/tasks.json that autoruns an obfuscated payload disguised as a Font Awesome .woff2 file, through an 8-month infection of three real GitHub repos (Binary-Mindz org). Using GitHub's server-side activity log they reconstruct 853 force-pushes showing the operators A/B-testing multiple concurrent payload variants (400/500/900), rewriting commits to impersonate legitimate cleanup commits, hiding payloads inside eslint.config.mjs and prisma.config.ts, and using an Ethereum-wallet-based C2 dead-drop (NullReceiver). The post lists why common detection heuristics (filename search, whitespace padding, marker strings) fail against the new variants and gives working detections (file-type checks, folderOpen task grepping, activity-log force-push monitoring) plus full IOCs.

VS CodeGitHubNode.js+2
PolinRiderDPRKContagious Interview+2

Threat Intel, Supply Chain, Blue Team & Detection, Malware & RE· Published and added 26 Sep 2026

github.comrepo🧠 AI

Hindsight — Agent Memory That Learns

Hindsight is an open-source agent memory system (MIT-licensed, self-hostable via Docker/Helm or usable as Hindsight Cloud) that goes beyond RAG-style recall by having agents learn through consolidated observations and mental models built from retained facts and experiences. It exposes retain/recall/reflect operations, a built-in MCP server per memory bank, Python/Node/Go/CLI clients, an LLM-wrapper for drop-in memory on OpenAI/Anthropic calls, and reports state-of-the-art results on the LongMemEval long-term memory benchmark, independently reproduced by Virginia Tech's Sanghani Center and The Washington Post.

Model Context ProtocolClaude CodeCodex+8
HindsightVectorize.ioLongMemEval+2

agents, mcp· Added 26 Sep 2026

thehackernews.comarticle🛡️ Security

Nearly 800 Malicious npm Packages Deliver Cross-Platform RAT and Infostealer

The Hacker News details a campaign of nearly 800 (later 1,033) malicious npm packages delivering the WEL1DROPPER downloader — dubbed Flooding Dropper by Sonatype — which fetches cross-platform RAT/infostealer payloads via Cloudflare Workers or DNS TXT-record fallback from wel1.ru, patches ETW/AMSI on Windows, and deploys the Sliver C2 framework on Linux. The piece also covers a related npm crypto-stealer campaign, multiple npm/PyPI packages tied to EtherHiding droppers and credential theft (Solana wallets, .env secrets, Discord/GitHub Actions tokens), and Chrome extensions abusing a bandwidth-sharing SDK to turn browsers into residential-proxy web scrapers.

npmCloudflare WorkersPyPI+3
WEL1DROPPERFlooding DropperMoika+8

Supply Chain, Malware & RE, Threat Intel· Added 26 Sep 2026

securityboulevard.comarticle🛡️ Security

973 MCP Packages, 71% Single-Maintainer: A Practitioner

Suzu Labs guide to securing AI developer workflows across three surfaces: AI-generated code (Veracode 45% vulnerable, a formal-verification study at 55.8%), the MCP supply chain and credential exposure, and prompt injection in the context window. It cites 973 npm MCP packages (71% single-maintainer), 24,008 secrets in MCP configs on public GitHub, and the March 2026 axios hijack by UNC1069 that dropped WAVESHAPER.V2 and tampered with MCP configs. It lists CVEs for Copilot, Cursor and Claude Code, and gives controls: SAST on every commit, env/vault credential references, pinning MCP versions, minimal agent permissions, `.cursorignore`/Claude deny rules, and monitoring IDE DNS traffic.

Model Context ProtocolnpmCursor+3
CVE-2025-53773CVE-2026-22708CVE-2025-55284+9

AI Security, Supply Chain, DevSecOps· Added 26 Sep 2026

arxiv.orgpaper🛡️ Security

CONTINUITY: Security-Context Contracts for Composable LLM Agent Controls

This paper identifies security-context discontinuity, a failure mode where individually correct LLM agent security mechanisms such as provenance tracking, authorization, policy enforcement, and protocol adapters fail to compose safely because security-critical context gets dropped, widened, rebound, or reinterpreted as actions cross component boundaries. The authors introduce CONTINUITY, a framework modeling each component with assume-guarantee contracts and carrying authenticated context via signed root grants, provenance commitments, role-bound transition receipts, and effect-bound execution permits, formalizing end-to-end consequence integrity. A reference verifier and cross-layer fault-injection suite covering 32 fault classes across four domains was evaluated on 2560 attack instances, 700 benign tasks, and 200 ambiguous cases, with the full configuration blocking all harmful effects while passing benign tasks and correctly escalating ambiguous ones.

LLM
CONTINUITY

AI Security· Added 26 Sep 2026

blog.trailofbits.comarticle🛡️ Security

Don't let TEEs break your MPC

Trail of Bits explains why running threshold-signature MPC protocols inside TEEs (Intel TDX, AMD SEV-SNP, AWS Nitro Enclaves) is not automatically secure: a malicious host can roll back enclave filesystem state to force reuse of deleted pre-signature nonces, leaking a signer's private key share. The post catalogs recurring audit pitfalls — incomplete attestation measurements (citing the WhatsApp Private Inference LD_PRELOAD bypass), missing verification steps, weak hardening, stale-backup/rollback risks (including LUKS2 header manipulation in confidential VMs), and physical/side-channel attacks like TEE Fail and DDRop against DDR5 memory — and gives best practices such as binding attestation to MPC party identities and using multiple TEE vendors for defense-in-depth.

Intel TDXAMD SEV-SNPAWS Nitro Enclaves+2
TEE FailDDRopWhatsApp Private Inference+1

Blockchain, Hardware & RF· Published and added 25 Sep 2026

blog.talosintelligence.comarticle🛡️ Security

Trust and the enticing consultancy offer

Talos's weekly Threat Source newsletter opens with a first-person account of a social-engineering scam targeting security professionals: an unsolicited $300 "consultancy" offer that escalates into pressure to extract non-public insights from employers, a pattern the author links to fake-recruiter/trojanized-job-offer schemes. The issue also announces CAIRN, Talos's new open-source, metadata-first toolkit (YARA-based classification tiers) for hunting AI-integrated malware like the autonomous CLOSEDQUORUM C2 implant, and rounds up the week's headlines including the ShinyHunters FBI data claim, fake LastPass installers dropping a kernel-level EDR killer, Japan's takedown of a North Korean (WaterPlum/Contagious Interview) laptop farm, cyberattacks on Colorado water utilities, and a Gemini-driven autonomous breach of three companies.

YARAGemini
WaterPlumContagious InterviewDPRK+6

Threat Intel, AI Security· Added 7 Oct 2026, published 24 Sep 2026

openai.comarticle🧠 AI

Introducing GPT-6 Sol and Luna

OpenAI introduces GPT-6 Sol and GPT-6 Luna, cheaper models trained with methods similar to GPT-6 Astra. API prices drop 50% against GPT-5.6 promotional pricing. The post reports cost-per-task comparisons against Claude Opus 5 and Fable 5/5.1: AutomationBench, Agents' Last Exam, FrontierCode, DeepSWE v1.1 (Sol 68.8%, Luna 66.6%) and OSWorld 2.0 offline. It also covers improved GPT-6 prompt caching (90% discount on cached reads, a dashboard, a diagnostics tool, explicit breakpoints, changing reasoning effort or tools without breaking the cache), factuality and alignment gains, and availability in ChatGPT Work, Codex and the API as `gpt-6-sol` and `gpt-6-luna`.

OpenAI APICodexChatGPT+1
OpenAIGPT-6 SolGPT-6 Luna+12

models, coding-agents, inference· Added 29 Sep 2026, published 22 Sep 2026

gambit.securitywriteup🛡️ Security

Autonomous AI Agents Hack Online Retailers for $25 a Company

Gambit Security recovered the staging server of a financially motivated actor running three open-source AI agent harnesses — Strix (vuln scanning), Cairn (autonomous exploitation), and Hermes (orchestration) — against hundreds of online retailers at a marginal cost of tens of dollars per target. The campaign exfiltrated 600,000+ credit card records via Magento database compromises, deployed checkout-page card skimmers on at least 19 confirmed and 100+ further sites, and in one case an agent's own cleanup routine dropped 180 database tables including victim backups. The report details full attack chains (SQLi to RCE to AWS Secrets Manager dump to card decryption), the AI harnesses' operating costs (~$25 mean per target on OpenRouter/opus-4.6/GLM/DeepSeek), and multiple real-world skimmer injection techniques.

StrixCairnHermes+3
Overwatch DataShadowserver FoundationDaniel Gordon+3

Threat Intel, AI Security, Offensive Security· Added 26 Sep 2026, published 22 Sep 2026

aikido.devwriteup🛡️ Security

Graphalgo campaign spreads to Terraform providers and Go Modules

Aikido documents the Graphalgo malware campaign's expansion beyond NPM into two malicious Terraform providers (gocommunity-io/dockerd and the kreuzwerker/docker typosquat kreuzwenker/docker) and two Go modules (gocommunity.io/orderedbtree, gogets.dev/btreex), marking the first observed systematic Terraform provider malware distribution. The payload is a Go port of Graphalgo sharing blockchain infrastructure, Slack C2, and a public key with prior JS/NPM samples; it activates only under specific hash-gated runtime conditions (targeted attack indicator), then deploys a Go RAT with dual C2 channels — an Ethereum (Arbitrum Sepolia) smart-contract dead drop and Slack bot messaging — plus self-delete and remote code execution capabilities. The threat actor also stood up two fake Go package ecosystem websites (gocommunity.io, gogets.dev) to socially engineer developers and backdated Git commits to obscure module publication timing.

TerraformGoSlack+3
GraphalgoReversingLabsSafedep+6

Supply Chain, Threat Intel, Blockchain· Published and added 22 Sep 2026

huggingface.coarticle🧠 AI

Transformers now runs llama.cpp quants

Hugging Face Transformers can now load GGUF quantized checkpoints directly via from_pretrained(gguf_file=...) and run them at near-llama.cpp speed on Apple Silicon by reusing ggml's Metal kernels through the kernels library, plus generation-loop optimizations such as dropping unnecessary attention masks and deferring stopping checks. The post benchmarks Qwen3.5 dense and MoE GGUF checkpoints against llama.cpp's llama-bench on an M2 Max, shows how to serve GGUF models with transformers serve as an OpenAI-compatible endpoint usable by clients like Jan or Pi, and covers dequantizing GGUF weights for fine-tuning via GgufConfig(dequantize=True). Current limitations: MPS-only packed inference, no batching support yet, and architecture coverage limited to Qwen3.5/Qwen3.8.

Hugging Face Transformersllama.cppGGUF+4
Hugging FaceQwen3.5Unsloth+12

inference, models· Added 29 Sep 2026, published 22 Sep 2026

huntress.comwriteup🛡️ Security

The Tale of Two INC Ransom Notes: A Ransomware Timeline | Huntress

Huntress details a post-incident investigation into an INC ransomware attack that hit 175+ endpoints, reconstructed from surviving EDR telemetry and Windows event logs rather than live detection. The intrusion shows a 17-day gap between initial scheduled-task persistence and RDP lateral movement (possibly an initial access broker), and a second wave using AnyDesk, a BYOVD tool (hwau.exe loading the HwAudio kernel driver) to disable security controls, and Impacket's atexec.py to deploy INC ransomware. Attackers dropped two distinct ransom notes 53 minutes apart: a standard INC-README.txt and a detailed DATALEAK_PRESS_RELEASE.txt threatening to notify media, employees and partners with a full inventory of stolen files.

AnyDeskImpacketPowerShell+3
INC ransomwareBYOVDnetscan.exe

Threat Intel, Blue Team & Detection· Added 22 Sep 2026, published 21 Sep 2026

socket.devwriteup🛡️ Security

Socket: Two Joyfill npm Beta Releases Compromised to Deliver DEV#POPPER Remote Access Trojan

Socket's research team found two beta releases of the @joyfill npm packages (@joyfill/layouts and @joyfill/components) contained an import-time JavaScript implant that resolves encrypted payloads through Tron, Aptos, and BNB Smart Chain transactions, ultimately dropping a 77KB Node.js remote-access trojan matching the DEV#POPPER family and sharing loader fingerprints with the PolinRider blockchain-loader campaign. The RAT establishes a Socket.IO C2 channel, executes arbitrary JS/shell commands, exfiltrates files and clipboard data, and persists by patching files inside VS Code, Cursor, Antigravity, Discord Desktop, GitHub Desktop, and the global npm CLI; a parallel detached-process branch fetches an additional bootstrap that can deploy a Python credential/browser-data stealer assessed as an OmniStealer variant. Because the implant fires on module load (not via npm lifecycle scripts), `--ignore-scripts` provides no protection, and the writeup includes full IOCs, blockchain addresses, C2 infrastructure, and MITRE ATT&CK mappings.

npmNode.jsPython+3
DEV#POPPERPolinRiderOmniStealer+12

Supply Chain, Malware & RE, Threat Intel· Added 22 Sep 2026, published 20 Sep 2026

newsletter.semianalysis.comarticle🧠 AI

Engrams Embedding Entendre: Codesign for Efficient DRAM/SSD Offloading

Engram is a DeepSeek model component that adds learned multi-token embedding lookups, and this SemiAnalysis report studies offloading its tables from HBM to host DRAM and SSD. On B300, DRAM offload let TP4 drop to TP2 and improved the pareto curve by up to 1.6x. On B200, DRAM beat SSD, with 121 million versus 52 million tokens per dollar near 125 tokens/s/user. The report also covers Engram ablations and InferenceX results across NVIDIA GPUs and MI355X.

vLLMCUDAMixture of Experts+2
SemiAnalysisDeepSeek-V4.1-FlashNVIDIA+6

inference, research, evals· Added 29 Oct 2026, published 18 Sep 2026

aikido.devarticle🛡️ Security

Betterleaks: Gitleaks creator's open-source secrets scanner successor

Betterleaks is a new open-source secrets scanner built by Gitleaks' original creator (now Head of Secrets Scanning at Aikido) as a drop-in replacement for Gitleaks. It adds CEL-based rule validation, a BPE-tokenization "token efficiency" filter that hits 98.6% recall on the CredData benchmark versus 70.4% for entropy-based detection, default double/triple-encoding handling, parallelized git repo scanning, and a pure-Go (no CGO/Hyperscan) implementation, with v2 plans for auto-revocation, permissions mapping, and LLM-assisted classification.

GitleaksBetterleaksAikido Security+1
CredData

DevSecOps· Added 18 Sep 2026

arxiv.orgpaper🧠 AI

Workspace Models: Lightweight Robotic Memory via Saliency-Driven Supervision

This paper introduces "workspace tokens," a lightweight latent memory representation for robotic manipulation policies that replaces expensive in-the-loop VLM queries. During training, a VLM identifies task-salient current and historical information, which is distilled into the workspace token via a set-reconstruction decoder loss; at deployment, the token serves as a drop-in replacement for raw observations. Experiments in simulation and on hardware show the approach improves policy performance on memory-intensive tasks while being far cheaper to run than VLM-in-the-loop methods.

Vision-Language Model

research, multimodal· Added 22 Sep 2026, published 17 Sep 2026

chainalysis.comarticle🛡️ Security

DPRK and Iran are Leading a 5.2x Surge YoY in Blockchain-Assisted Cyberattacks

Chainalysis research on blockchain dead drops (BDD), the practice of storing malware C2 payloads and configuration pointers on public blockchains (EtherHiding and its variants) so infrastructure survives takedowns. It details three attributed case studies: DPRK linked UNC5342 using a TRON and Aptos to BSC cross-chain relay to deliver crypto-stealing malware via fake job interviews, Iran-nexus actors embedding C2 in Bitcoin OP_RETURN transactions tied to a Satoshi-era address, and a Russian-language Malware-as-a-Service operation running resolver contracts on Polygon across dozens of downstream customers. It reports a 420 to 440 percent YoY surge in BDD activity, attributes it partly to unrestricted open-weight Chinese LLMs lowering the barrier to entry, and maps the technique to MITRE ATT&CK T1102.002.

BitcoinBinance Smart ChainTRON+2
EtherHidingDPRKUNC5342+5

Threat Intel, Blockchain· Added 30 Sep 2026, published 17 Sep 2026

opensourcemalware.comwriteup🛡️ Security

WeaselBiscuit Strips BeaverTail and OtterCookie Down to Essentials

OpenSourceMalware researchers detail WeaselBiscuit, a newly discovered lightweight JavaScript infostealer found hidden in 11+ npm packages (e.g. process-tailwind, engin1, the @biz44 scope), which shares tradecraft with DPRK-linked BeaverTail/OtterCookie but strips out wallet-draining, password decryption, and remote-shell features. The writeup walks through the full infection chain - a package auto-running a detached Node loader, fetching a Base64-encoded second stage from Npoint dead-drop URLs, and beaconing to a hardcoded HTTP C2 (103.170.217.184:8787) - plus its capabilities (Chrome extension-storage theft, clipboard capture, Windows keylogging) and a campaign-cluster graph tying packages together via shared hashes and resolver URLs. Attribution to DPRK is explicitly labeled a tentative hypothesis rather than confirmed.

npmNode.jsChrome
WeaselBiscuitBeaverTailOtterCookie+3

Supply Chain, Threat Intel, Malware & RE· Published and added 17 Sep 2026

group-ib.comwriteup🛡️ Security

HEAVYGRAM: A Telegram-based Surveillance Backdoor Linked to Handala Hack

Group-IB documents previously undocumented samples of HEAVYGRAM, a Python/PyInstaller-based Windows backdoor that uses the Telegram bot API for command-and-control, screen/audio capture, data exfiltration, and DLL side-loading, alongside the related CRUDEEXCLUDE loader that adds Windows Defender exclusions. The research corroborates and extends a March 2026 US DOJ affidavit and FBI FLASH report, attributing the malware with moderate confidence to the Handala Hack persona — assessed as a false-flag "hacktivist" front for Void Manticore (aka Storm-0842/Banished Kitten), operating on behalf of Iran's MOIS — used since Fall 2023 against Iranian dissidents, journalists, and critics of the Iranian government via Telegram-delivered, Delphi-packaged lures (fake KeePass, Telegram, Pictory apps). It details four infection-chain variants (WSF/VBS downloaders, HTA Telegram-polling scripts, Delphi droppers with embedded archives), the implant's command prefixes (@@/**/##) and attachment handlers, dual-bot C2 configurations, and provides IOCs and detection/hardening recommendations.

TelegramPowerShellPython+3
Handala HackVoid ManticoreStorm-0842+12

Threat Intel, Malware & RE· Added 1 Oct 2026, published 17 Sep 2026

github.comrepo🛡️ Security

Shai-Hulud-2.0-Detector — npm supply-chain compromise scanner

Shai-Hulud-2.0-Detector is a GitHub Action and CLI tool that scans package.json/lockfiles for packages compromised in the Shai-Hulud 2.0 (Nov 2025) and ChainDrop (Aug 2026) npm supply-chain worms. It uses semver-precise matching against a database of 1,241+ known-compromised package versions (auto-updated daily from Datadog and Wiz Research feeds) to flag malicious preinstall/postinstall droppers (setup_bun.js, Math_Symbol.js), rogue GitHub self-hosted runners named SHA1HULUD, and ChainDrop's new IDE-persistence hooks in .claude/settings.json and .vscode/tasks.json. It ships SARIF output for GitHub Security tab integration, an allowlist system, and a detailed incident-response guide covering credential rotation and forensic checks.

npmGitHub ActionsBun+3
Shai-Hulud 2.0ChainDropkeyv+6

Supply Chain, DevSecOps, Blue Team & Detection· Added 16 Sep 2026

endorlabs.comarticle🛡️ Security

Malicious Code in Open Source: How to Detect It Before You Ship | Blog | Endor Labs

Endor Labs explains the two dominant classes of OSS malware attacks - dependency/name confusion (typosquatting, combo-squatting, brand-jacking) and attacks on legitimate packages/maintainers - and how the OpenSSF malware-analysis project sandboxes new PyPI/npm releases and reports confirmed malware to OSV. It walks through real cases it detected, including the chunked/split-across-files PyPI malware ttlo and gisi, and Whatfuscator which drops and runs a PyInstaller-built Windows executable, plus two false-positive suspicious-code flags (versioneer 0.29, azure-functions 1.18.0) caused by benign base64/zlib obfuscation.

PyPIPythonnpm+3
ttlogisiWhatfuscator+5

Supply Chain· Published and added 11 Sep 2026

endorlabs.comwriteup🛡️ Security

Shai-Hulud 2 Malware Campaign Targets GitHub and Cloud Credentials Using Bun Runtime | Blog | Endor Labs

Endor Labs' live incident tracker for the Shai-Hulud 2.0 npm supply-chain worm that began around Nov 24, 2025, compromising packages from Zapier, ENS Domains, Postman and PostHog. It details the infection chain (malicious preinstall script, setup_bun.js dropper, obfuscated bun_environment.js payload), TruffleHog-style credential theft from AWS, GCP, Azure, GitHub and npm, self-replication via stolen npm and GitHub tokens, a self-hosted GitHub Actions runner backdoor abusing repository Discussions for command injection and C2, and destructive wiper behavior that shreds the user's home directory on Windows and Linux.

npmBunGitHub Actions+3
Shai-Hulud 2.0Shai-HuludZapier+3

Supply Chain, Threat Intel, DevSecOps· Published and added 11 Sep 2026

wiz.ioadvisory🛡️ Security

Artifactory Under Attack: In-the-Wild Exploitation of CVE-2026-42016, CVE-2026-42018 & CVE-2026-82329

Wiz Research documents active in-the-wild exploitation of three JFrog Artifactory vulnerabilities: CVE-2026-42018 (exposes an internal anonymous-user JWT via POST /access/api/v1/aws/token/), CVE-2026-42016 (token scope validation flaw allowing that JWT to be escalated to admin via POST /access/api/v1/tokens), and CVE-2026-82329 (unauthenticated admin access via POST /access/api/v1/registry/join, added to CISA KEV). Attackers chained the first two to create persistent admin accounts, deploy malicious Groovy plugins for RCE, and drop Rust-based C2 backdoors, while CVE-2026-82329 was exploited independently for configuration exfiltration, cluster join-key theft, and credential/SSH-key persistence. The post includes exact request sequences, detection signatures, affected/fixed version ranges, and remediation guidance.

JFrog ArtifactoryRust
CVE-2026-42016CVE-2026-42018CVE-2026-82329+1

AppSec, Threat Intel, Blue Team & Detection· Published and added 10 Sep 2026

arxiv.orgpaper🧠 AI

Data Scarcity and Model Sparsity: Mixtures-of-Experts Overfit More to Repeated Data

This paper studies how Mixture-of-Experts (MoE) language models respond to repeated training data compared to dense Transformers, across models from 80M to 1B active (8.5B total) parameters. It finds MoEs overfit to repeated data much faster than dense models — degrading noticeably at 4x repetition versus 8x for dense models — with the effect scaling with total (not active) parameter sparsity, and shows that dropout and masking-based regularization can partially mitigate this while MoE routing stabilization and expert specialization correlate with the overfitting.

TransformerMixture-of-Experts

research, training· Added 22 Sep 2026, published 10 Sep 2026

blog.talosintelligence.comwriteup🛡️ Security

Active exploitation of Cisco Secure Firewall Management Center vulnerabilities

Cisco Talos details active exploitation of CVE-2026-20079 (CVSS 10.0 unauthenticated auth bypass leading to root) and CVE-2026-20316 (low-privilege login via static credentials) in Cisco Secure Firewall Management Center. Three post-compromise clusters are tracked: UAT-12197 deploying a JSP web shell and JAR command executor to exfiltrate credentials; UAT-11823, overlapping with Sandworm, using a malicious Makeself license.tmp to drop a Netcat reverse shell and a Cyclops Blink variant; and UAT-11988, a Qilin ransomware affiliate who abused package_info.pl for LOTL recon, SOCKS5/reverse-SSH tunneling, and ultimately deployed Qilin ransomware. Talos provides Snort SIDs, hotfix guidance ahead of a comprehensive hardening release, and a GitHub IOC repository.

Cisco Secure Firewall Management CenterImpacketInvoke-TheHash+3
CVE-2026-20079CVE-2026-20316UAT-12197+6

Threat Intel, Offensive Security· Added 7 Oct 2026, published 9 Sep 2026

huntress.comwriteup🛡️ Security

Grand Theft Auto VI hype leads to malware

Huntress analyzed a fake GTA6 game ISO (some padded to 100GB+ with junk data) distributed via SEO poisoning, gaming forums, and torrents ahead of the game's real release. The ISO's "installer" drops a Russian-language crack-themed installer that stages multiple NJRAT copies, a DCRAT implant, the Mercurial Grabber infostealer (exfiltrating browser/Discord/Roblox/Minecraft data via Discord webhooks), Chaos ransomware repurposed as a destructive wiper (with a fake "license not found" error to mask the compromise), and an unexplained Yandex Browser install. The writeup includes IOCs (C2 IPs, ngrok tunnel, hosts-file modifications, malicious Discord webhook URL) and notes current Windows Defender detects the components.

WindowsWindows DefenderMicrosoft Edge
NJRATDCRATMercurial Grabber+2

Malware & RE, Threat Intel· Added 11 Sep 2026, published 9 Sep 2026

blog.talosintelligence.comwriteup🛡️ Security

ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager

Cisco Talos reconstructs two related WebDAV-based infection chains (tracked actor UAT-10820) that use a ClickFix fake-CAPTCHA lure, EtherHiding on BNB Smart Chain to stage JavaScript via a malicious Cloudflare Worker, and WebDAV-delivered disguised DLLs executed via rundll32 ordinal calls to drop the Amatera stealer. Depending on the C2 configuration, Amatera then deploys either a NativeAOT-loaded ZigCryptoStealer with a BYOVD EDR-killer driver and a Go-based Yamux reverse proxy, or a PowerShell stager that installs a trojanized NetSupport Manager RAT pointed at Russian C2 infrastructure. The post details loader internals, Amatera's dead-drop C2 resolution via Telegraph and Steam, and provides ClamAV signatures plus a full IOC list.

WebDAVPowerShellGo+3
UAT-10820AmateraZigCryptoStealer+8

Threat Intel, Malware & RE, Blockchain· Added 7 Oct 2026, published 8 Sep 2026

github.comrepo🧠 AI

headroomlabs-ai/headroom

Headroom is an open-source (Apache 2.0) local compression layer that sits between AI agents and LLM providers, compressing tool outputs, logs, RAG chunks, files and conversation history before they reach the model. It offers a Python/TypeScript library, a drop-in proxy, an `headroom wrap` mode for popular coding agents (Claude Code, Codex, Cursor, Copilot, Aider, etc.), an MCP server, cross-agent shared memory with dedup, and output-token reduction via verbosity steering and effort routing — all running locally with reversible compression (CCR) so originals stay retrievable.

Model Context ProtocolClaude CodeCodex+6
HeadroomKompress-v2-baseSerena+3

ai-infra, coding-agents, mcp· Added 23 Sep 2026, published 7 Sep 2026

aikido.devwriteup🛡️ Security

MECCHA CHAMELEON can't hide from the RCE

Aikido researchers found a delayed RCE in the Unreal Engine 5-based game MECCHA CHAMELEON, exploitable via a malicious Steam Workshop map. A Blueprint-exposed audio recording function allowed arbitrary file writes via path traversal, a null-byte trick stripped the auto-appended .wav extension to drop an .exe into the Windows Startup folder, and PCM audio samples were crafted byte-for-byte to smuggle a polyglot WAV/HTA payload that launches mshta.exe and runs arbitrary code on reboot. The issue was patched in the game's 4.0.0 update.

WindowsAikido SecurityUnreal Engine
MECCHA CHAMELEONSteam Workshopmshta.exe+3

AppSec, Offensive Security· Published and added 3 Sep 2026

huntress.comwriteup🛡️ Security

Rogue ScreenConnect Installations Across Unrelated Hosts Suggest Worm-Like Activity

Huntress details a campaign in which social-engineering (tech-support scams, Quick Assist, malicious downloads) leads to rogue ScreenConnect installs that deploy a four-stage VBScript loader (1.vbs–4.vbs). The loader profiles the host (checking for EDR products, existing ScreenConnect, RAM size), fetches an AES-encrypted payload via a Dropbox-hosted map file, and drops one of three packages: a user-level backdoor, a persistence/privesc kit, or a tunneling+cryptomining bundle (wstunnel/XMRig plus the vulnerable WinRing0 driver for BYOVD). A backdoored ScreenConnect client then re-pushes the VBScript chain to every newly connected Host session via ScreenConnect's file-transfer API, giving the campaign worm-like self-propagation — which ConnectWise later confirmed stems from CVE-2026-84869, a 9.9 CVSS flaw in unauthorized file-transfer execution, patched in ScreenConnect 26.6.5.

ScreenConnectPowerShellWindows Defender+3
CVE-2026-84869XMRigBYOVD+1

Threat Intel, Malware & RE, Blue Team & Detection· Added 8 Sep 2026, published 3 Sep 2026

huntress.comwriteup🛡️ Security

The Crypto Wallet That Never Opened: Tampered Exodus Installer Hides a Modular RAT

Huntress dissects a trojanized Exodus crypto wallet installer (v24.33.4, unsigned MSI built with WiX) that installs a genuine wallet but patches Electron's show()/focus()/center() methods so no window ever appears, then loads a modular RAT via a hand-written reflective PE loader implemented in JavaScript using the Node.js koffi FFI library. The RAT (VNC, SOCKS proxy, browser-credential stealer, recon module) beacons over WebSockets and uses Azure Table Storage as a dead-drop C2 channel to blend into legitimate cloud traffic, while delivery abuses double-extension .pdf.js phishing, ZIP-staged JS files, and an unused search-ms/WebDAV technique; the writeup also covers multi-layer string-array/arithmetic deobfuscation and includes full IOCs and mitigation guidance.

ExoduskoffiWindows+3
ClickFix

Malware & RE, Threat Intel, Blue Team & Detection· Added 3 Sep 2026, published 1 Sep 2026

pgj11.comwriteup🛡️ Security

pgj11: Analysis of Bincrypter and gsocket (gs-netcat)

Deep-dive reverse engineering of a real-world incident where a WordPress site compromised via CVE-2026-18322 was used to drop a bincrypter-obfuscated, statically-linked gs-netcat (gsocket) 1.4.42beta5 binary as a reverse-shell tunnel, persisted via crontab and masquerading as "netd"/"[kthreadd]". The author fully unravels bincrypter's multi-stage shell obfuscation (character-separator tricks, AES-256-CBC/openssl decryption, memfd_create fileless ELF execution via a Perl one-liner) and reveals a custom THC UPX build with zeroed magic bytes/PackHeader used to hide payload identification, along with gsocket's self-embedded XOR-encoded operator configuration. Releases two open-source tools (Bincrypter-Extract, Gsocket-Config-Extract), YARA rules, and an ImHex pattern file, plus full IOCs (C2 IP, GSRN secret, process/memfd artifacts).

gsocketbincrypterWordPress+3
CVE-2026-18322THChackerschoice+4

Malware & RE, Threat Intel, Offensive Security· Published and added 31 Aug 2026

aikido.devarticle🛡️ Security

Securing Docker images

Aikido Security's guide to hardening Docker images explains where container vulnerabilities come from (base OS layers like Debian/glibc that ship far more than an app needs), citing CVE-2023-4911 (Looney Tunables in glibc) and the xz-utils backdoor as cautionary examples for version-pinning decisions. It lays out hardening steps such as multi-stage builds, removing unused packages, non-root users, read-only filesystems, dropping Linux capabilities, pinning base images by digest, generating SBOMs, and signing/verifying images, then pitches Aikido Images, which backports CVE patches onto the same pinned base image version instead of forcing a migration to a new hardened distro.

DockerNode.jsDebian+2
CVE-2023-4911xz-utils

DevSecOps, Supply Chain· Added 3 Sep 2026, published 28 Aug 2026

huntress.comadvisory🛡️ Security

PaperCut Zero-Day: Active Exploitation and Pre-Auth RCE

Huntress details active exploitation of an authorization-bypass flaw in PaperCut NG/MF (CVE-2026-81578) chained with an unsafe dynamic class-loading vulnerability in the database connection utilities (CVE-2026-82078) to achieve unauthenticated remote code execution in the PaperCut Application Server. The writeup covers Huntress's own observed intrusions (base64-encoded recon commands, dropped Java .class payloads decompiled with Fernflower, log-wiping behavior, and an Apache Derby pwn database indicator), a reproduced PoC achieving SYSTEM-level code execution via pc-app.exe, and detailed patching, evidence-preservation, and hunting guidance across PaperCut's staged emergency patches.

PaperCutWindows
CVE-2026-81578CVE-2026-82078pc-app.exe

Threat Intel, AppSec, Blue Team & Detection· Added 3 Sep 2026, published 28 Aug 2026

huggingface.coarticle🧠 AI

Wire It, Run It, Deploy It: AI Workflows in Gradio

This Hugging Face blog post introduces gr.Workflow, a Gradio primitive that lets developers describe an AI pipeline as a graph of typed nodes (references for inputs, operators for steps, subjects for outputs) and get a runnable drag-and-drop canvas, an auto-generated REST API per output, and one-command deployment to Hugging Face Spaces from the same definition. Operator nodes can call Hugging Face Inference Providers, other Gradio Spaces, Hub dataset rows, or plain Python functions decorated with @spaces.GPU for in-Space GPU inference via ZeroGPU. Worked examples include an image-editing pipeline using Qwen-Image-Edit, a multi-model media studio chaining FLUX, background removal, and TTS, a parallel fan-out image-generation demo, a Hugging Face dataset profiler using the Datasets Server API, and a GPU-based image animator using Lightricks/LTX-Video via Diffusers.

GradioHugging FacePython+3
Hugging Face SpacesHugging Face Inference ProvidersQwen-Image-Edit+5

llm-apps, ai-infra· Added 29 Sep 2026, published 25 Aug 2026

stepsecurity.ioarticle🛡️ Security

The State of Open Source Supply Chain Attacks

StepSecurity's threat intelligence team's annual report tallies 56 confirmed software supply chain attacks between August 2025 and August 2026, showing an over 8x acceleration since February 2026 driven by self-propagating worms (Shai-Hulud, Shai-Hulud 2.0, CanisterWorm, Miasma, ChainDrop) and mutable GitHub Actions tags. It details the five-day TeamPCP campaign that stole 78,330 secrets from 2,186 organizations by poisoning Trivy Action, Checkmarx KICS, telnyx, and LiteLLM, plus compromises spanning npm, PyPI, RubyGems, Composer, and crates.io.

npmGitHub ActionsPyPI+3
Shai-HuludShai-Hulud 2.0CanisterWorm+22

Supply Chain, DevSecOps, Threat Intel· Added 3 Sep 2026, published 23 Aug 2026

stepsecurity.iowriteup🛡️ Security

Rust Supply-Chain Attack: arrayref, internment, and append-only-vec Poisoned by the proc-macro1 Build-Time Dropper

StepSecurity's forensic writeup on a compromised crates.io maintainer account that published poisoned releases of arrayref (245M downloads), internment, and append-only-vec, each pulling in proc-macro1, a typosquat of proc-macro2 impersonating David Tolnay whose build.rs silently drops and executes a cross-platform stage-2 payload at compile time. The attacker also mass-yanked clean arrayref versions to funnel Cargo's "yanked" warning toward the one poisoned release, and StepSecurity reproduced the attack in GitHub Actions with Harden-Runner, capturing the C2 callback to 23.254.165.112:9089 and demonstrating automatic blocking via a global IOC block list. The post includes the full attack timeline, dropper base64-obfuscated URL scheme, SHA-256 hashes, C2 IOCs, and remediation/detection guidance for lockfiles and CI caches.

RustCargocrates.io+3
arrayrefinternmentappend-only-vec+15

Supply Chain, DevSecOps· Added 3 Sep 2026, published 22 Aug 2026

orca.securityadvisory🛡️ Security

Critical Elementor Pro File Upload Flaw Enables Unauthenticated Remote Code Execution on WordPress Sites

CVE-2026-32475 (CVSS 9.0) is an unauthenticated arbitrary file upload leading to RCE in Elementor Pro's Forms module (versions up to 4.2.1), caused by the extension-blocklist check and the file-move step running in two separate loops with different empty-file handling, letting a two-part file submission bypass the blocklist and drop a PHP webshell into the public wp-content/uploads/elementor/forms/ directory. The post also flags related WordPress core CVE-2026-65640 (CVSS 8.8, fixed in 7.0.4), an Author-level RCE via malicious PostScript upload requiring Imagick and Ghostscript. Fix: upgrade Elementor Pro to 4.2.2+ and WordPress core to 7.0.4, and audit the uploads/elementor/forms directory for planted PHP files.

WordPressPHPOrca Security+1
CVE-2026-32475CVE-2026-65640arbitrary file upload+1

AppSec· Added 3 Sep 2026, published 20 Aug 2026

aikido.devwriteup🛡️ Security

Popular Rust crates arrayref, append-only-vec, and internment compromised in Supply Chain Attack

Aikido researchers detail a supply-chain compromise of three popular Rust crates maintained by the same author, arrayref with 244M downloads, append-only-vec with 4M, and internment with 14M, that were modified to add a single malicious manifest dependency, proc-macro1, a typosquat of proc-macro2. Because the dependency's build.rs executes automatically during cargo build, merely compiling a project pulling in any of these crates downloads and runs a platform-specific payload that drops an infostealer targeting Chromium browser credentials and crypto-wallet extension storage, installs macOS LaunchAgent persistence, and beacons to a lightweight C2 supporting remote shell commands. The campaign's TTPs closely mirror the prior npm-based Axios and Mastra compromises attributed to DPRK, suggesting the same actor expanding into the Rust ecosystem.

RustCargocrates.io+3
proc-macro1proc-macro-endroundy+4

Supply Chain, Malware & RE, Threat Intel· Added 3 Sep 2026, published 20 Aug 2026

huntress.comwriteup🛡️ Security

Post-DEF CON Phishing Uses Malicious Google Doc to Deliver Malware

Huntress researchers document a phishing campaign targeting Black Hat/DEF CON attendees via X DMs impersonating a CoinDesk exec, luring victims into opening a weaponized Google Doc with a custom Google Apps Script sidebar that runs a fake "decryption" flow before delivering ClickFix-style commands or a manual "update" that drops malware. On macOS this delivers AMOS infostealer plus a LaunchDaemon-based polling backdoor with SOCKS5 proxy capability; a follow-up fake DocSend/Dropbox installer delivers a ClickOnce/NSIS loader chain on Windows that installs NetSupport RAT, a process-hollowed rogue Certificate Authority that MITMs VirusTotal traffic, and an incomplete Ledger wallet-targeting implant. The piece includes deep technical detail on the loader's C2 protocol, stolen/fraudulent code-signing certificates, and infrastructure patterns (multi-branded loader domains), plus mitigation guidance and a link to published IOCs.

Google WorkspacePowerShellNetSupport Manager+3
AMOS stealerClickFixSleestak+1

Threat Intel, Malware & RE· Added 3 Sep 2026, published 19 Aug 2026

depthfirst.comarticle🛡️ Security

Introducing dfbench v1: A cybersecurity benchmark for frontier models and agentic systems | depthfirst

dfbench v1 is depthfirst's held-out benchmark for AI agents doing defensive security work: 253 examples, 910 real vulnerabilities, 17 languages and 27 weakness classes. It scores detection recall, validation precision (estimated with a Kaplan-Meier "hotspot" analysis) and differential analysis across commits. Results show recall rising as precision falls for stronger models, and "closed" recall dropping at higher thinking levels.

LLMGitHub
dfbenchdepthfirstCyberGym+4

AI Security, AppSec· Added 29 Oct 2026, published 19 Aug 2026

huntress.comwriteup🛡️ Security

MacSync Stealer: How a Google Search for Claude Led to a macOS Infostealer

Huntress SOC analysts reverse-engineer MacSync, a macOS infostealer/RAT distributed via a sponsored Google Ads link to a fake "Apple Support"-branded claude.ai shared conversation that uses ClickFix to trick victims into pasting a curl/zsh loader into Terminal. The six-stage chain runs a polymorphic gzip/Base64 loader, an in-memory AppleScript stealer that harvests Chromium Safe Storage keys, keychain secrets, Telegram/SSH/cloud credentials, abuses TCC (Full Disk Access and Screen Recording) prompts, drops a Mach-O RAT with WebSocket/TLS C2 and an XOR-obfuscated fallback domain, and trojanizes 84 crypto wallet extensions/apps to phish seed phrases. The piece also compares it to prior AMOS Stealer and SectopRAT ClickFix campaigns and offers behavior-based detection guidance.

macOSAppleScriptzsh+3
MacSyncClickFixSectopRAT+2

Malware & RE, Threat Intel, Blue Team & Detection· Added 3 Sep 2026, published 17 Aug 2026

Showing 150 of 230

Show more