 Earliest Known PolinRider Malware Found in 2025 npm Packages
OpenSourceMalware traces nine itsa-* npm package versions published on 4 May 2025 from a hijacked maintainer account to the PolinRider campaign, eight months before documented victims. It decodes the EtherHiding chain (BNB Smart Chain and Ethereum calldata, JADESNOW, INVISIBLEFERRET bootstrapper, Socket.IO RAT, Python stealer) and links the 2025 sample to 2026 force-push infections. It lists IOCs, hashes, a timeline and hunting guidance.
 opensourcemalware.comwriteupPublished and added 30 Oct 2026🛡️ Security
 NIK C2: The new AI-enabled command-and-control framework
NIK C2 is a newly observed C2 framework with a Go-based 64-bit Windows implant that embeds an OpenAI Chat Completions client (ai_generate command), falling back to the victim's OPENAI_API_KEY. Talos details its 52+ commands, AES-256-GCM over WebSocket with HTTP fallback, credential, wallet and keystroke theft, screen-lock ransomware, AMSI bypass and anti-debug. It also lists a live C2 at 87.120.196[.]120 and total-sitevv[.]lol.
 blog.talosintelligence.comwriteupPublished and added 29 Oct 2026🛡️ Security
 Searchjacked: Hidden Browser Extensions Hijack Searches for 13 Million Users
Searchjacked is Socket's research on 319 browser extensions (about 13.44M users over a decade) that hijack searches to earn ad revenue. The fetched text attributes 200 extensions to named operators such as Intango, System1, Perion, Mutual Media and Kinner Lake, and 119 to unknown operators like "SecuryBrowse" and "Bing-Search". It lists the Yahoo and Bing monetization IDs used to link them. The narrative and technical mechanics are not in the fetched text.
 socket.devwriteupPublished and added 29 Oct 2026🛡️ Security
 Malicious Firefox Extensions Impersonate Phantom, Jupiter, and Bitget to Steal Wallet Secrets
Socket analysis of three malicious Firefox add-ons impersonating Phantom, Jupiter and Bitget wallets, using Unicode homoglyph names. They steal seed phrases and private keys and send them to brand-named subdomains of bonto[.]io. The Phantom fake adds a runtime loader that fetches and evals a second stage, and bundles a drainer backend with Telegram forwarding. Includes IOCs, hashes and wallet addresses.
socket.devwriteupPublished and added 27 Oct 2026🛡️ Security- Tailworm – Tailscale Vulnerabilities
Tailworm is a security assessment report by Erica Windisch (Cyberdione Labs) on Tailscale v1.104.2 and headscale v0.29.5, tested 22-24 October 2026. It documents 11 findings: Tailscale SSH unix-socket forwarding that runs as root (bind, dial and TOCTOU races), conn25 app-connector egress bypass, gliderssh memory exhaustion, serve/funnel flaws and headscale DoS. It includes PoC references, mitigations and fix status as of 27 October 2026. The page is truncated, so the later sections were not read.
 tailworm.comwriteupAdded 27 Oct 2026, published 25 Oct 2026🛡️ Security
 New Evidence Shows LiteLLM Secret-Stealing Workflows Ran 11 Days Before Supply Chain Attack
Socket's Threat Research team reports that malicious cache.yml workflows ran in the BerriAI/litellm repository on 10 and 12 October 2026, eleven days before the 21 October release attack that published litellm==1.107.0. Each commit pushed to a short-lived ci-tmp-<hex> branch, then deleted it, sending base64-encoded CI secrets to webhook.site. Evidence comes from Actions metrics and environment deployment records; 20 secret names were exposed.
socket.devwriteupPublished and added 23 Oct 2026🛡️ Security From JavaScript to Renderer Code Execution: Three V8 Vulnerabilities and Two v8CTF Flags | depthfirst
Depth First Security's write-up describes three V8 bugs found using its dfs-large1 research tooling: CVE-2026-78938, a type confusion in Promise.prototype.finally that lets an internal helper be constructed and return a primitive; CVE-2026-79236, a TurboFan load-elimination bug that keeps a stale property-array pointer after object migration; and a shared WebAssembly memory sandbox escape (issue 546253900) caused by mismatched backing-store registration during serialization. It walks through turning each memory bug into addrof/fakeobj primitives, chaining either with the sandbox escape to reclaim a freed V8 isolate via a WebSocket allocation, and pivoting through a CFI-constrained ROP chain to achieve Chrome renderer code execution, earning two v8CTF flags. Fixes landed between August 20 and 25, 2026.
 depthfirst.comwriteupAdded 29 Oct 2026, published 20 Oct 2026🛡️ Security
 ARMORY CASTLE Exploits BeyondTrust
ARMORY CASTLE (formerly UNC5221), a suspected PRC-nexus actor, exploited BeyondTrust Remote Support zero-day CVE-2026-102764 in August 2026, per Mandiant incident response. The post details the SAWFLY PHP webshell, BARECLAW SOCKS5 WebSocket tunneler, SUID root escalation, sudoers template persistence, vault credential extraction, log deletion and haproxy.conf changes. It adds YARA rules, detection ideas and patch-first remediation (BT26-05).
 cloud.google.comwriteupAdded 29 Oct 2026, published 15 Oct 2026🛡️ Security
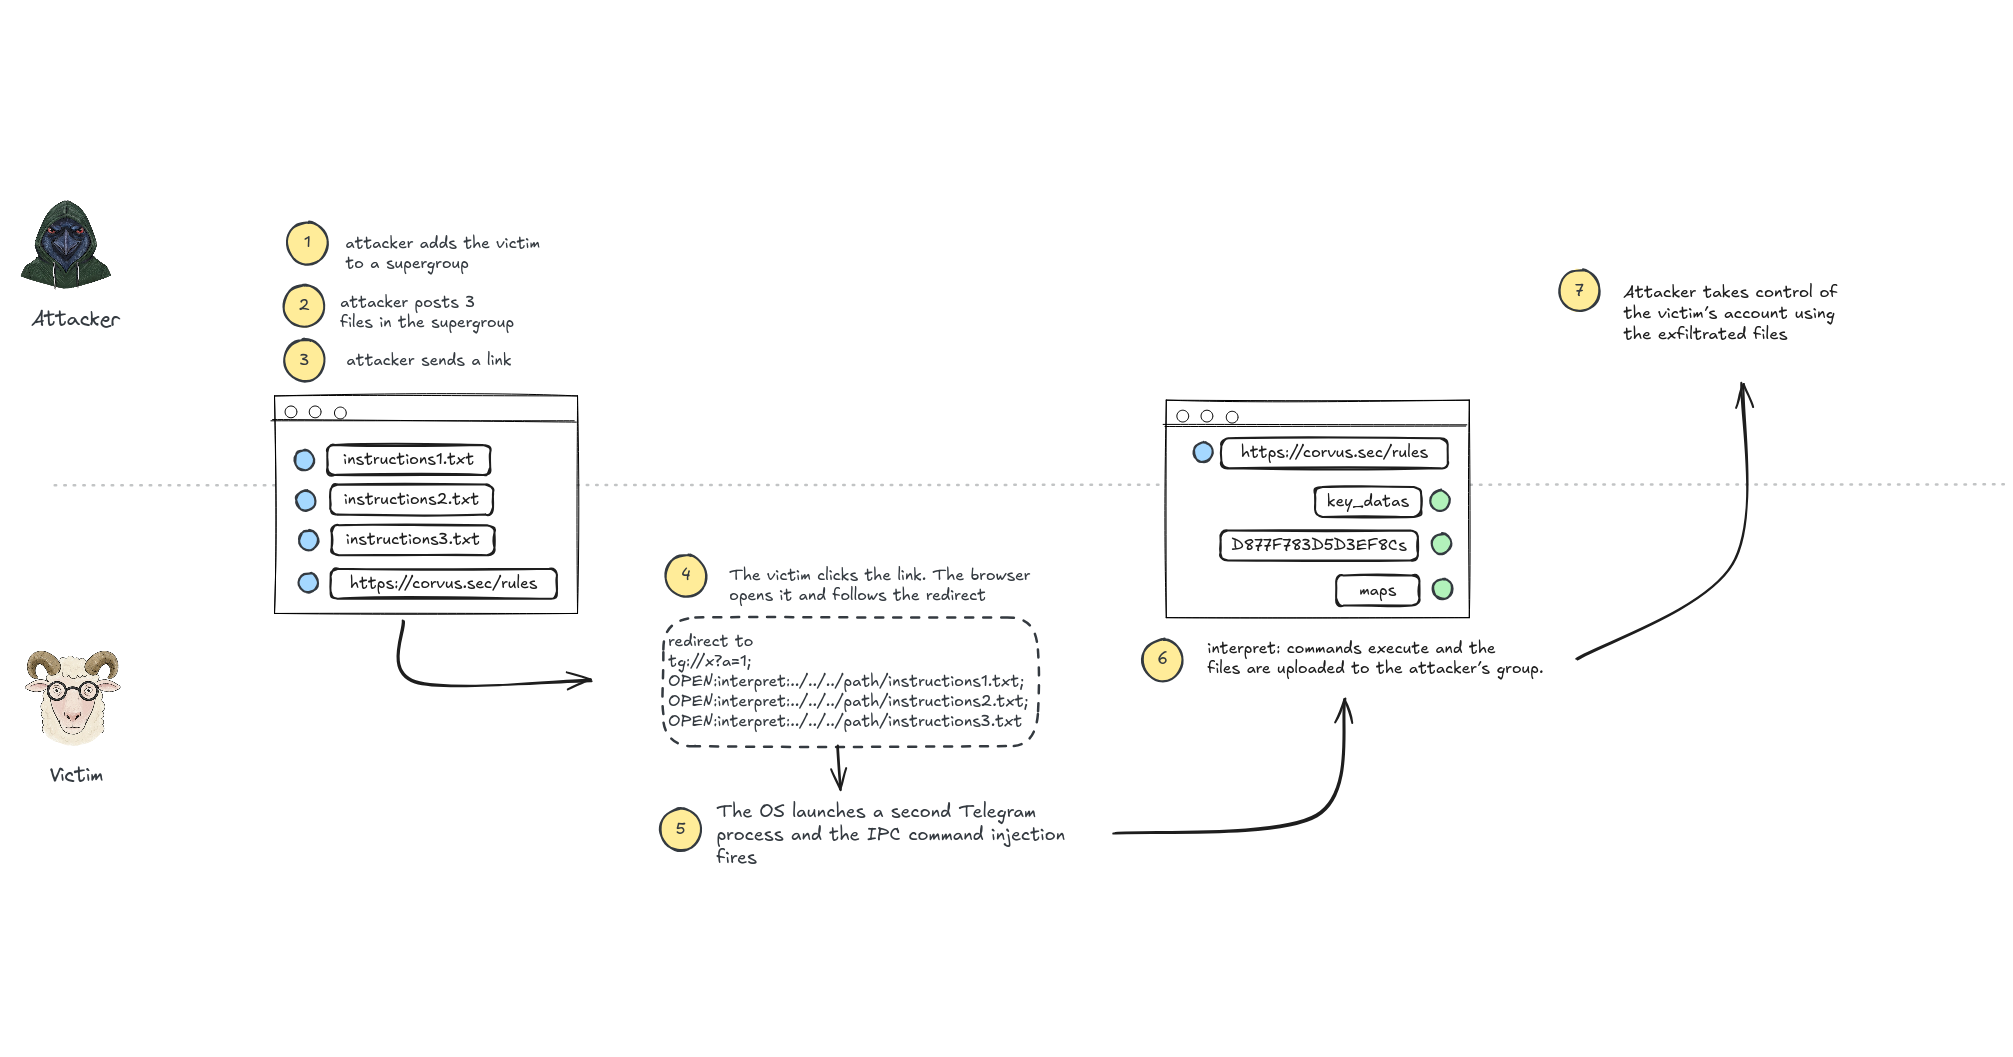 Telegram Desktop vulnerability allowed any user's file to be stolen
Writeup of a two-bug chain in Telegram Desktop: the single-instance local-socket IPC does not escape the semicolon record separator, so a clicked tg:// link injects extra OPEN: commands, which reach the internal interpret: scheme (InterpretSendPath) that reads an arbitrary file and sends it to a chat with no authorization or confirmation. The author plants instruction files via auto-download in a group, then exfiltrates tdata/key_datas and session files (no local passcode means an empty-password KEK) to take over the account. Fixed in 7.2.9 by removing interpret: and escaping separators; the post lists mitigations such as a local passcode and restricting who can add you to groups.
 beaksec.github.iowriteupPublished and added 10 Oct 2026🛡️ Security
 New GhostAction Wave Hits Hundreds of Repos, Expanding Beyond CI/CD Secrets to Cloud Credentials
Socket documents an October 8, 2026 wave of the GhostAction campaign in which two compromised GitHub maintainer accounts (henrywoo and kitao) pushed a malicious security-audit.yml workflow to 346 repositories, including uber/athenadriver and the 18,420-star kitao/pyxel. Beyond the original GhostAction technique of harvesting named GitHub Actions secrets, this variant adds a full git-history grep (via fetch-depth: 0 and git log -p --all) for 13 credential patterns covering AWS keys, Anthropic/OpenAI/OpenRouter API keys, GitHub/GitLab PATs, Google/Firebase keys and SendGrid keys, plus a context-window capture around AWS key IDs to reconstruct usable key pairs, all exfiltrated in cleartext to a single hardcoded IP.
socket.devwriteupPublished and added 9 Oct 2026🛡️ Security UAT-11985: AI-assisted event lures delivering real-time Google AitM phishing
Cisco Talos details UAT-11985, a spear-phishing campaign against Taiwan-based research organizations (impersonating institutions like the Taiwan European Union Centre and NCCU Institute of International Relations) that used AI-assisted, templated lure emails and poster-based QR code phishing (quishing) to drive victims to a real-time adversary-in-the-middle phishing kit. The kit impersonates Google sign-in across zh-CN/zh-TW/en locales, uses a split HTTP-POST/WebSocket architecture to mirror Google's live authentication flow and dynamically push MFA challenge screens, enabling full session-token theft and MFA bypass. Talos attributes the kit's localization architecture and lexical choices to a Simplified Chinese-speaking developer and publishes ClamAV/Snort coverage plus IOCs on GitHub.
blog.talosintelligence.comwriteupPublished and added 8 Oct 2026🛡️ Security- TensorLake npm SDK Compromised in ChainDrop Shai-Hulud Credential-Stealing Attack
Socket.dev reports that TensorLake's npm SDK was compromised as part of the ChainDrop campaign, a variant/wave of the Shai-Hulud credential-stealing npm worm. The compromised package reportedly harvests developer credentials from infected systems, continuing the pattern of self-propagating npm supply-chain attacks seen across the Shai-Hulud family. Full technical detail could not be verified in this pass due to a content-processing failure.
socket.devwriteupPublished and added 8 Oct 2026🛡️ Security  16 Malicious Firefox Extensions Steal Cryptocurrency Wallet Credentials
Socket Threat Research uncovered a coordinated campaign of 16 malicious Firefox extensions split into a Rabby Wallet clone family (4 extensions, full repackaged Rabby codebase) and an OKX Wallet-impersonating "Portal WALLET" family (12 extensions), all hooking wallet import flows to steal mnemonic seed phrases and private keys and exfiltrate them via GET/POST/sendBeacon to attacker-controlled Cloudflare Workers endpoints under the icy-star-f45c.workers.dev namespace. The writeup includes campaign markers (EQOx7EIPZSNi), background.js SHA-256 hashes, extension IDs/XPI hashes, and ties the activity to a prior August 2026 crypto-theft extension campaign Socket tracked, plus concrete detection and incident-response guidance.
socket.devwriteupPublished and added 7 Oct 2026🛡️ Security Pretty Themes, Hidden Loaders: GlassWorm-Linked Extensions Span VS Code Marketplace and Open VSX
Socket's Threat Research team uncovered a theme-extension cluster spanning four VS Code Marketplace and six Open VSX listings, including two confirmed malicious extensions: Aurora Nocturne Night Theme (a Windows downloader that fetches and silently executes temp_batch.cmd via cmd.exe from fingercakes4sale[.]store, tied to XWorm C2 infrastructure) and Cosmic Nebula Themes, whose app.js decrypts an AES-256-CBC embedded stage and uses a Solana transaction memo as a dead-drop to resolve follow-on payload infrastructure — the same AES key, Solana address, and execution model previously documented in GlassWorm activity. Git commit identities, near-identical theme source, shared Russian-language developer comments, and brandjacking (Coca-Cola, Aurora Borealis name-squatting) link the cluster together; a Dec 14, 2025 DEV Community article is assessed as promotional infrastructure driving Open VSX installs. The post provides full IOCs (hashes, domains, Solana address, AES key/IV, GitHub accounts) and MITRE ATT&CK mappings for defenders to hunt and inventory extensions across both registries.
socket.devwriteupPublished and added 2 Oct 2026🛡️ Security- Determined Attacker Uploads Malicious Webshells to Parks and Rec Management Platform Servers
Huntress details a four-act intrusion against a shared parks-and-recreation management platform running on IIS, where an attacker first tried noisy unauthenticated exploits (IIS 8.3 tilde enumeration, WebDAV verb abuse, upload-handler bypasses) before simply registering a member account and uploading .aspx webshells via a member-file upload feature across three servers. The attacker enumerated hosts, extracted web.config/connection strings, hunted for cardholder data (Fortis/MXMerchant webhook logs, CVV/card-number strings), then escalated to timestomping, re-deploying known-filename webshells, and finally injecting an AI-generated PowerShell/JS dropper into a trojanized jQuery file to turn site visitors' browsers into WebRTC/WebSocket C2 clients (ririmochii/bubuneeko Cloudflare Workers infrastructure). Includes a zh-CN PowerShell user-agent string used for attribution and full command/IOC listings useful for detection engineering.
 huntress.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security
 NeedyMantis: Unpacking a post-compromise malware family used in targeted operations
Microsoft Threat Intelligence documents NeedyMantis, a previously unreported modular post-compromise malware family used in targeted intrusions against telecoms, universities, medical nonprofits, intergovernmental organizations, and government contractors. The writeup details a multi-stage C++/x64 shellcode loader chain delivered via DLL sideloading (abusing Poedit, curl, TightVNC, Vim, and spoofed Office/Broadcom/Intel/NVIDIA DLLs), a custom encrypted/compressed archive format, a minimized custom PE-like executable format, and a WebSockets-based C2 protocol with RC4 key exchange and modular load/unload commands. Microsoft links observed use to Storm-3069 (tied to the Kaspersky-reported DAEMON Tools supply chain compromise) and China-nexus activity, and provides IOCs, Defender detections, and KQL/Sentinel hunting queries.
 microsoft.comwriteupAdded 7 Oct 2026, published 28 Sep 2026🛡️ Security
 Re-Enabled GitHub Actions Expose Thousands of Repositories to Mini Shai-Hulud
Socket reports that the actions-cool/issues-helper and actions-cool/maintain-one-comment GitHub Actions, compromised in the May 2026 Mini Shai-Hulud campaign and disabled by GitHub, were re-enabled on September 16, 2026 with their release tags still pointing to the malicious code. Any workflow referencing them by tag (about 15,000 dependents for issues-helper alone) resumed running the Bun-executed obfuscated payload. Workflow run logs show the switch from fast "Repository access blocked" failures to multi-minute successful runs. The post gives remediation: SHA-pin actions, rotate secrets, and hunt for oven-sh/setup-bun and bun run index.js in runner logs. An update says both repos were disabled again on September 25.
socket.devwriteupPublished and added 24 Sep 2026🛡️ Security Malicious Firefox Extension Poses as PDF Identity Verifier to Hijack Google Accounts
Socket's Threat Research team dissects a malicious Firefox extension (pdf-para-texto@extensao.local, "PDF Identity Verifier") that ships with no hardcoded malicious code — all attack logic is fetched as data into browser.storage.local after install via a lookalike domain (pdf.gusercontent.com), evading static store review. Once armed, it abuses Google's FedCM API to silently identify the victim, injects a live automation script into real accounts.google.com pages to drive an invisible account-takeover flow (bypassing password entry, forcing passkey challenges, dodging Google's bot detection, and forcing/capturing a password reset), while a webRequest listener steals the oauth_token session cookie from Set-Cookie headers — giving the attacker both a live session and a durable new password. The campaign targets Portuguese- and Spanish-speaking users starting September 2026 and includes full IOCs (domains, file hashes) and remediation steps.
socket.devwriteupPublished and added 23 Sep 2026🛡️ Security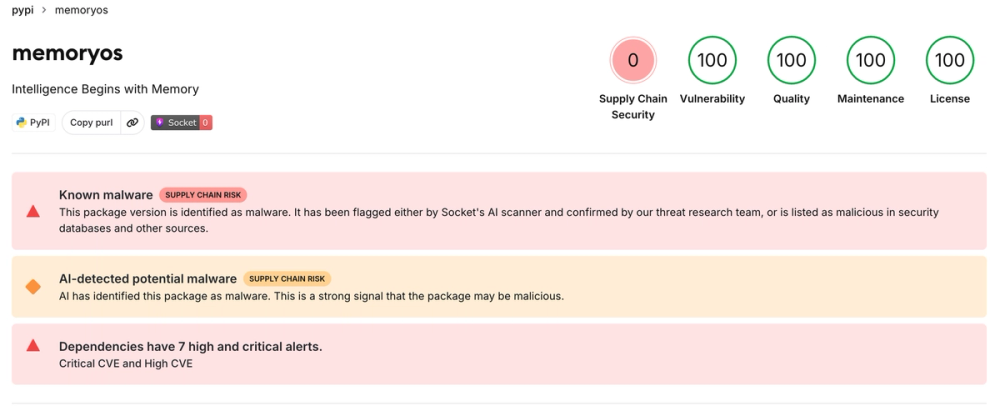 MemTensor npm and PyPI Packages Compromised in Credential-Stealing Supply Chain Attack
Socket details a supply-chain compromise of MemTensor's MemOS packages: npm package @memtensor/memos-cloud-openclaw-plugin (versions 0.1.21, 0.1.23, 0.1.25) and PyPI package MemoryOS (2.0.34), both published as the latest release on their registries. Each malicious release bundles a stripped, statically-linked Go binary called sckit that launches on import/plugin-load, scans $HOME for npm, PyPI, GitHub, GitLab, AWS, Vault and SSH credentials, and exfiltrates them to C2 servers under skyleen[.]fr, with the npm variant also capturing OpenClaw agent prompt text and the code additionally showing potential worm-like republish capability using stolen registry tokens.
socket.devwriteupPublished and added 23 Sep 2026🛡️ Security- Compromised npm Packages in the AsyncAPI Namespace Deliver Miasma Botnet Loader
Socket's Threat Research Team details a supply-chain compromise of four @asyncapi npm packages (generator-helpers, generator-components, generator, specs) published via a poisoned source commit through GitHub Actions trusted publishing. The packages contain an obfuscated load-time (not install-hook) implant that spawns a detached Node.js process to fetch an IPFS-hosted, AES-256-GCM-encrypted loader delivering the "Miasma" botnet/tasking framework, which supports REST C2, multi-channel comms (Nostr, IPFS, Ethereum RPC, BitTorrent DHT), shell execution, file exfiltration, and systemd persistence. Includes full technical analysis, IOCs, hashes, and MITRE ATT&CK mapping.
socket.devwriteupAdded 21 Sep 2026🛡️ Security 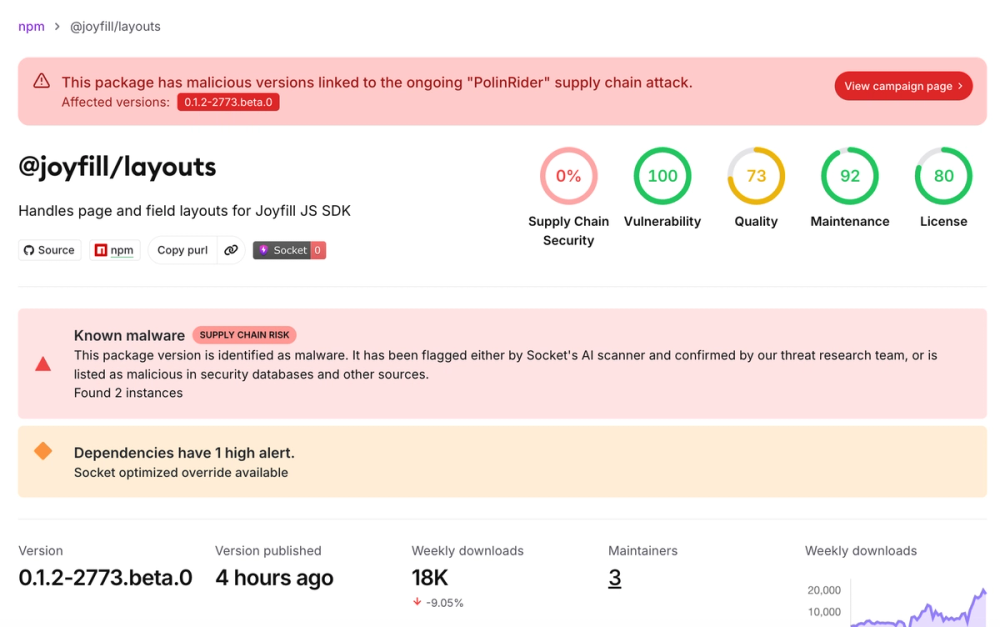 Socket: Two Joyfill npm Beta Releases Compromised to Deliver DEV#POPPER Remote Access Trojan
Socket's research team found two beta releases of the @joyfill npm packages (@joyfill/layouts and @joyfill/components) contained an import-time JavaScript implant that resolves encrypted payloads through Tron, Aptos, and BNB Smart Chain transactions, ultimately dropping a 77KB Node.js remote-access trojan matching the DEV#POPPER family and sharing loader fingerprints with the PolinRider blockchain-loader campaign. The RAT establishes a Socket.IO C2 channel, executes arbitrary JS/shell commands, exfiltrates files and clipboard data, and persists by patching files inside VS Code, Cursor, Antigravity, Discord Desktop, GitHub Desktop, and the global npm CLI; a parallel detached-process branch fetches an additional bootstrap that can deploy a Python credential/browser-data stealer assessed as an OmniStealer variant. Because the implant fires on module load (not via npm lifecycle scripts), `--ignore-scripts` provides no protection, and the writeup includes full IOCs, blockchain addresses, C2 infrastructure, and MITRE ATT&CK mappings.
socket.devwriteupAdded 22 Sep 2026, published 20 Sep 2026🛡️ Security- Living Inside the Shell: zsh Modules on macOS
A DFIR researcher shows how macOS's default shell, zsh, ships with loadable modules (zsh/net/tcp, zsh/mapfile, zsh/attr, zsh/stat, zsh/sched) that let the shell itself open raw TCP sockets, read/write files, and manipulate extended attributes like com.apple.quarantine without spawning curl, xattr, rm, or nc. The post walks through a full example using ztcp and source /dev/fd/$fd to fetch and execute a second-stage payload directly from a socket (bootstrapping a LaunchAgent) with no downloaded file on disk and no child process, referencing the prior real-world use of zsh/net/tcp for reverse shells (documented by ESET and GTFOBins). It then validates via eslogger/Endpoint Security that DELETEEXTATTR/SETEXTATTR and similar operations remain visible even when performed through zsh builtins, arguing detections should target the underlying OS event rather than the specific binary invoked.
 dfir.chwriteupPublished and added 16 Sep 2026🛡️ Security
 ParaShells: Parallels Desktop Turns Appliance Install Into a Root Shell
JFrog researchers detail ParaShells, a local privilege escalation chain in Parallels Desktop 26.4.0 (build 57513) on Apple silicon that lets an unprivileged macOS user gain root. The chain combines a world-writable Unix socket for prl_disp_service, weak peer-credential-based authentication in PrlSrv_LoginLocal, and argument injection in the InstallAppliance extraction path where a crafted sVmParentPath breaks Qt's QProcess::splitCommand quoting to inject tar's --use-compress-program= flag, causing macOS tar to execute an attacker script as uid 0.
 jfrog.comwriteupPublished and added 15 Sep 2026🛡️ Security
 Socket: Malicious Extensions Drain Axiom Trade and Padre Crypto Sessions
Socket's Threat Research team identified six malicious Chrome and Firefox extensions (J7Tracker, VREO, Orbit Tracker, GhostApe, GhostApe Color) that steal authenticated session tokens, Firebase access tokens, and wallet-related data from users of the Axiom Trade and Padre crypto trading platforms. The extensions abuse a byte-identical collection module (axiom-fetch-intercept.js) that reads localStorage/IndexedDB and exfiltrates data by encoding it into URLs opened via browser navigation to Vercel-hosted C2 endpoints, evading manifest-based host-permission review since navigation isn't subject to CORS/CSP connect-src restrictions. The report includes full IOCs (extension IDs, C2 domains, hashes), attribution links via shared code and publisher portfolios, and defender guidance for hunting and blocking the campaign.
socket.devwriteupPublished and added 12 Sep 2026🛡️ Security Socket: "JeetBot" Twitch Extension Steals 31,000 Users' OAuth Tokens
Socket's Threat Research Team analyzed "Twitch Enhanced Viewer | JeetBot", a Chrome/Firefox extension with 31,000 users that captures the user's live Twitch OAuth session token from the Authorization header and forwards it as an &auth= query parameter to proxy servers operated by JeetBot, a Russian-language Twitch/Kick/VK-Live bot SaaS, exempting only ten hardcoded Russian streamer channels. Earlier v4.x builds POSTed tokens outright to dedicated set-token endpoints (with backups on deno.dev/deno.net) and included Russian-language comments indicating deliberate rate-limited exfiltration; the account-scoped bearer token grants chat, whispers, and settings access, contradicting both store listings' "no data collection" claims. Firefox has since shipped a fix (85.8.7) after Socket's disclosure; the Chrome build remained vulnerable at publication.
socket.devwriteupPublished and added 12 Sep 2026🛡️ Security Machine speed, hold the AI: hand-rolled marimo CVE-2026-39987 exploit
Sysdig's Threat Research Team documents a hand-coded (non-LLM) exploitation of CVE-2026-39987, a pre-authentication RCE in marimo notebooks caused by a missing validate_auth() check on the /terminal/ws WebSocket endpoint. The operator chained credential theft from environment variables and Redis, AWS Secrets Manager retrieval, and SSH pivoting to a bastion host in eight seconds, ignored a planted prompt-injection honeypot meant to detect LLM agents, and left behind reusable base64-encoded boto3/paramiko toolkits in /tmp. The post includes full script reproductions, IOCs (IPs, file paths, AS63949/Linode infrastructure), CloudTrail/GuardDuty detection guidance, and remediation steps (patch to marimo 0.23.0, restrict the terminal endpoint, scope Secrets Manager access).
 sysdig.comwriteupAdded 20 Sep 2026, published 11 Sep 2026🛡️ Security
- The Crypto Wallet That Never Opened: Tampered Exodus Installer Hides a Modular RAT
Huntress dissects a trojanized Exodus crypto wallet installer (v24.33.4, unsigned MSI built with WiX) that installs a genuine wallet but patches Electron's show()/focus()/center() methods so no window ever appears, then loads a modular RAT via a hand-written reflective PE loader implemented in JavaScript using the Node.js koffi FFI library. The RAT (VNC, SOCKS proxy, browser-credential stealer, recon module) beacons over WebSockets and uses Azure Table Storage as a dead-drop C2 channel to blend into legitimate cloud traffic, while delivery abuses double-extension .pdf.js phishing, ZIP-staged JS files, and an unused search-ms/WebDAV technique; the writeup also covers multi-layer string-array/arithmetic deobfuscation and includes full IOCs and mitigation guidance.
huntress.comwriteupAdded 3 Sep 2026, published 1 Sep 2026🛡️ Security  Socket: FUNNULL iOS Spyware Campaign via 13 Malicious Packagist Themes
Socket's Threat Research Team traced 13 malicious Composer/Packagist theme packages (across vsmov, vsphim, haiau009, chilltvcms, ophimcms vendors) used by Vietnamese movie/comic streaming sites, which inject JavaScript running an ad-fraud/gambling redirect on all mobile visitors and, on unpatched iPhones, chain WebKit exploits (CVE-2025-31277, CVE-2025-43529) through a GPU-process pivot into a kernel escape via the AppleM2ScalerCSCDriver IOKit client (related to CVE-2026-43655) to install spyware. The payload exfiltrates keychain data, SMS, photos, contacts, and — after an August 2026 redeployment — directly steals crypto wallet seeds/mnemonics from Bitget, Phantom, Trust Wallet, and others. The report attributes delivery infrastructure to FUNNULL (Triad Nexus, OFAC-sanctioned operator Liu Lizhi), ties the exploit kit to the "DarkSword" iOS exploit family, and provides full IOCs, hashes, and MITRE ATT&CK mapping.
socket.devwriteupPublished and added 1 Sep 2026🛡️ Security- pgj11: Analysis of Bincrypter and gsocket (gs-netcat)
Deep-dive reverse engineering of a real-world incident where a WordPress site compromised via CVE-2026-18322 was used to drop a bincrypter-obfuscated, statically-linked gs-netcat (gsocket) 1.4.42beta5 binary as a reverse-shell tunnel, persisted via crontab and masquerading as "netd"/"[kthreadd]". The author fully unravels bincrypter's multi-stage shell obfuscation (character-separator tricks, AES-256-CBC/openssl decryption, memfd_create fileless ELF execution via a Perl one-liner) and reveals a custom THC UPX build with zeroed magic bytes/PackHeader used to hide payload identification, along with gsocket's self-embedded XOR-encoded operator configuration. Releases two open-source tools (Bincrypter-Extract, Gsocket-Config-Extract), YARA rules, and an ImHex pattern file, plus full IOCs (C2 IP, GSRN secret, process/memfd artifacts).
 pgj11.comwriteupPublished and added 31 Aug 2026🛡️ Security
 Socket: "Superior" Campaign
Socket researchers uncovered 19 Chrome and Edge extensions (18 Chrome, 1 Edge) delivering a modular wallet-drainer and credential-stealing framework, tracked as the "Superior" campaign and linked to a 2024 operation first reported by DomainTools and Secure Annex. Threat actors either build extensions from scratch or buy established ones (like "Enable Right Click & Copy — Smart Unlock + OCR" with ~80,000 combined users) and later push malicious updates that strip CSP headers via declarativeNetRequest, open an AES-GCM-encrypted WebSocket C2 channel, and inject JavaScript payloads that phish hardware-wallet seed phrases, hijack wallet-connect flows, harvest exchange session tokens, and serve ClickFix-style fake browser-update lures. The post includes full code snippets, a breakdown of 16+ malicious modules, and a large IOC list of C2 domains and extension IDs.
socket.devwriteupPublished and added 28 Aug 2026🛡️ Security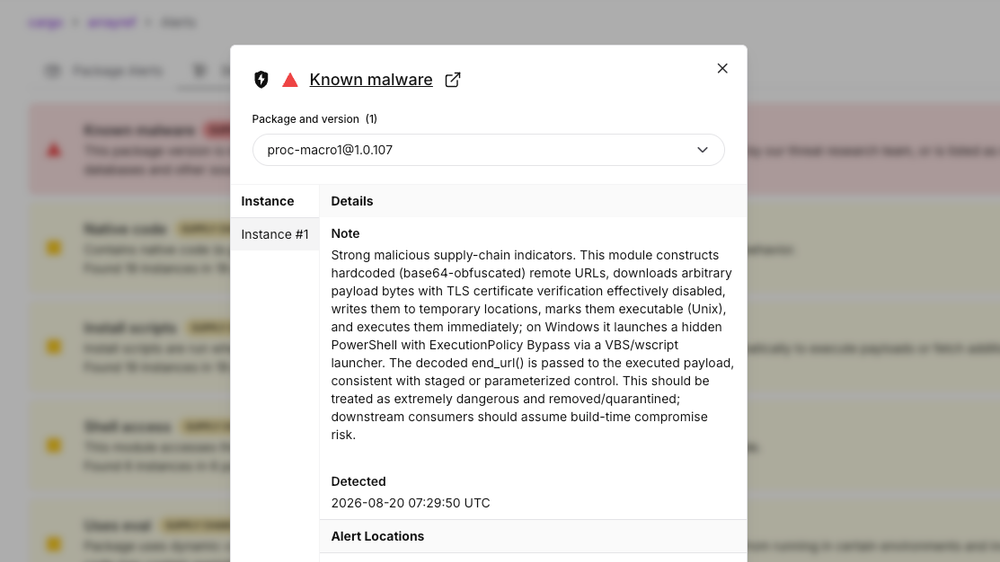 Socket: Popular Rust Crates Compromised in Build-Time Supply Chain Attack
Socket's Threat Research Team documents a supply chain attack in which three legitimate Rust crates (arrayref, internment, append-only-vec) maintained by droundy were republished with a dependency on proc-macro1, a typosquat of proc-macro2 whose build.rs downloads and executes cross-platform malware during Cargo compilation. The stage-2 backdoor profiles the host, inventories Chromium browser login origins and extensions, establishes user-level persistence (HKCU Run key, systemd service, or LaunchAgent), and beacons to a C2 with a DGA fallback of ten date-based domains, with all analyzed variants sharing the same embedded RSA key. The report includes full IOCs (C2 IPs, payload hashes, host artifacts, DGA domains) and remediation guidance for CI/CD and developer environments that built the malicious versions.
socket.devwriteupPublished and added 20 Aug 2026🛡️ Security Socket: "Offside Wallet Theft Factory"
Socket's Threat Research team tracked 77 linked Firefox extension identities in a campaign dubbed "Offside Wallet Theft Factory": 40 are confirmed malicious (impersonating OKX, Rabby Wallet, TronLink and others) and 37 are deceptive sports-score shell extensions later repurposed into wallet stealers. Techniques include Supabase-controlled remote phishing switches, Cloudflare Worker exfiltration of recovery phrases, modified Rabby Wallet code that exfiltrates serialized keyrings via persistAllKeyrings() before local encryption, and hardcoded C2 servers stealing credentials and clipboard data. The post includes full SHA-256/IOC listings and shows how extension identities are repurposed over version history from benign utilities into wallet-draining malware.
socket.devwriteupPublished and added 19 Aug 2026🛡️ Security- MacSync Stealer: How a Google Search for Claude Led to a macOS Infostealer
Huntress SOC analysts reverse-engineer MacSync, a macOS infostealer/RAT distributed via a sponsored Google Ads link to a fake "Apple Support"-branded claude.ai shared conversation that uses ClickFix to trick victims into pasting a curl/zsh loader into Terminal. The six-stage chain runs a polymorphic gzip/Base64 loader, an in-memory AppleScript stealer that harvests Chromium Safe Storage keys, keychain secrets, Telegram/SSH/cloud credentials, abuses TCC (Full Disk Access and Screen Recording) prompts, drops a Mach-O RAT with WebSocket/TLS C2 and an XOR-obfuscated fallback domain, and trojanizes 84 crypto wallet extensions/apps to phish seed phrases. The piece also compares it to prior AMOS Stealer and SectopRAT ClickFix campaigns and offers behavior-based detection guidance.
huntress.comwriteupAdded 3 Sep 2026, published 17 Aug 2026🛡️ Security  Socket: 737 Malicious VPN/Proxy Chrome Extensions Impersonate 66 Brands
Socket's Threat Research Team documents a 737-extension Chrome Web Store campaign ('Myxa VPN' / Муха VPN) that impersonates 66 legitimate VPN/privacy brands (Proton VPN, NordVPN, AmneziaVPN, AntiZapret, Cloudflare 1.1.1.1, etc.) to lure Russian-speaking users seeking censorship circumvention. The extensions force all browser traffic through a shared SOCKS5 proxy pool via chrome.proxy.settings, evade DNS-based blocklists using DNS-over-HTTPS to resolve proxy hosts, sell non-existent premium server locations, ship fake license checks, add remote-configuration code post-approval, and submit false 'no data collection' justifications to Chrome reviewers. The report ties the operation to a single Russian self-employed-registered VPN business via shared Yandex Metrika counters, build-path leakage, bulk domain registration, and a Telegram-based billing dashboard, and notes 516 of the 737 extensions remain live despite prior Palo Alto Networks disclosure.
socket.devwriteupPublished and added 12 Aug 2026🛡️ Security PolinRider Caused Dozens of npm, Go, PHP Compromises
OpenSourceMalware's research ties together JFrog's, Nextron's, and Socket's separate reports on compromised html-to-gutenberg/fetch-page-assets npm packages, 16 Go modules, and Joyfill's poisoned beta releases, attributing all of them to DPRK's PolinRider campaign via shared XOR keys, TRON/Aptos wallets, C2 infrastructure, and the fa-solid-400.woff2 loader file hash. The piece argues these aren't targeted account takeovers but automated propagation from infected maintainer machines (via temp_auto_push.bat git history rewriting and stolen .npmrc tokens), and uses GH Archive to prove that 43 of 64 analyzed Go module pseudo-version timestamps were forged to appear years older than the actual malicious push. Delivered payloads include InvisibleFerret/DEV#POPPER RAT and the OmniStealer Python infostealer, and the article links a PolinRider crossover into a compromised Packagist/PHP package (roberts/leads) via shared C2 infrastructure.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security Compromised npm Packages: @joyfill/components and @joyfill/layouts Ship an Obfuscated Remote Access Trojan
StepSecurity dissects malicious beta versions of @joyfill/components and @joyfill/layouts published to npm on July 28, 2026, which inject a five-stage obfuscated payload that executes on import rather than via a postinstall hook, so npm install --ignore-scripts does not stop it. The chain resolves its C2 server by reading a transaction on the Tron blockchain (with Aptos as fallback), decrypts a BNB Smart Chain transaction to find the next stage, and deploys a Socket.IO remote access trojan with worm-like self-propagation that patches the global npm CLI, VS Code/Cursor's @vscode/deviceid module, Discord desktop, and GitHub Desktop, plus a Python credential stealer targeting browser data, wallets, and Git/GitHub tokens. The writeup includes fully deobfuscated source code, IOCs (C2 IPs, Tron addresses, file hashes), and results from detonating the packages under Harden-Runner in a sandbox.
 stepsecurity.iowriteupAdded 3 Sep 2026, published 30 Jul 2026🛡️ Security
- Reverse Engineering the Six Stages of MacSync Stealer and RAT
Huntress reverse-engineers MacSync, a macOS stealer-and-RAT chain delivered via a weaponised claude.ai share link promoted through Google Ads malvertising, where a victim searching for how to install Claude on a Mac pastes a curl piped to zsh one-liner. The writeup traces all six stages: a polymorphic zsh loader, a server-side AppleScript that social-engineers Full Disk Access and validates the account password via dscl authonly, keychain and browser Safe Storage theft, a statically-linked C++ Mach-O RAT with WebSocket and AES-CBC C2 plus LaunchAgent persistence disguised as legitimate updaters, a signed Screen Recording-badged helper that phishes the TCC screen-capture permission, and trojanised Electron wallet apps (Ledger Live and Ledger Wallet) that inject a fake recovery-phrase phishing flow. It ties the kit to the AMOS and Atomic Stealer lineage via Russian-language code comments and shared infrastructure, and documents concrete IOCs including domains, C2 IP, mutex naming, and plist patterns for defenders.
huntress.comwriteupAdded 3 Sep 2026, published 29 Jul 2026🛡️ Security  Socket: Distributed npm Package Cluster Delivers Cross-Platform RAT Targeting Alibaba Developers
Socket researchers uncovered a coordinated npm campaign using 15+ packages that impersonate private Alibaba (@ali scope) packages to trick internal developers into installing dependencies. Malicious functionality is split across the dependency chain (lure packages, smart-config-manager, cloud-config-fetcher, local-config-parser) so no single package looks malicious, ultimately fetching a remote config and executing rules via Node's vm module to deploy a cross-platform RAT with data exfiltration, command execution, and DingTalk-based lateral movement capabilities.
socket.devwriteupPublished and added 29 Jul 2026🛡️ Security Socket: Fake Corepack Site Distributes Infostealer and Proxyware to Developers
Socket's Threat Research team analyzed corepack[.]org, a fake site impersonating the Node.js Corepack tool that exploits its 2025 removal from Node.js bundling to rank in search results and trick developers into downloading a fake VPN installer. The installer drops OpenShield (an infostealer with browser-data/SSH-key theft, PowerShell execution, and run-key persistence) plus a bandwidth-sharing proxyware component that turns victim machines into proxy exit nodes, while a second click path delivers adware/trojan activity via OperaGXSetup.exe. The post includes full IOCs and details community/OpenJS Foundation takedown efforts against the domain.
socket.devwriteupPublished and added 25 Jul 2026🛡️ Security INC RANSOMWARE: THREAT INTELLIGENCE
A researcher deanonymizes INC ransomware's Tor negotiation panel (incpaykabjqc2mtdxq6c23nqh4x6m5dkps5fr6vgdkgzp5njssx6qkid.onion) to a real IP (178.20.41.208, Russia, nginx/Yii PHP backend) running on unusual port 1002, then reverse-engineers the panel's bundled React/Redux/Socket.io JavaScript to map its API endpoints, socket events, JWT-based auth, and leak/ransom-tracking features. The piece also correlates nine clearweb domains and ~170 IPs used by the group over 2023–2025 (65% Russia-hosted, CDN rotation patterns, Cloudflare fronting on one domain) and analyzes 108 ransomware builder samples to infer RaaS versioning, a 2024 forum sale, and links to spin-off groups Lynx and Sinobi.
 theravenfile.comwriteupAdded 3 Sep 2026, published 24 Jul 2026🛡️ Security
 Socket: GitHub Actions Abuse Powers Distributed cPanel/WHM Exploitation Campaign
Socket researchers traced malicious dev versions of ten Packagist packages owned by developer dinushchathurya back to compromised GitHub repositories containing 55-62 malicious GitHub Actions workflow files each. The workflows execute on GitHub-hosted Ubuntu runners on every push, download an architecture-matched Linux payload from C2 server 43.228.157.68, and run an internet scanner (`ipscan --exploit CVE-2026-41940`) that exploits an authentication bypass in cPanel/WHM and harvests cloud, database, SSH, and source-control credentials, exfiltrating results via heartbeat/results HTTP endpoints and DNSHook callbacks. GitHub code search for the campaign's unique markers returned 6,100-16,000 matching workflow files across unrelated repositories, indicating the abuse extends far beyond the one compromised maintainer and effectively weaponizes GitHub Actions as free, disposable attack infrastructure.
socket.devwriteupPublished and added 23 Jul 2026🛡️ Security Socket: Coordinated npm/PyPI Campaign Typosquats Paysafe, Skrill, Neteller Payment SDKs
Socket found 17 typosquatted npm and PyPI packages mimicking Paysafe, Skrill, and Neteller payment SDKs that steal secrets from environment variables and exfiltrate to an ngrok C2 server.
socket.devwriteupPublished and added 16 Jul 2026🛡️ Security Socket: Operation Muck and Load
Socket details "Operation Muck and Load," a campaign starting with a malicious Go module (github.com/kaleidora/dnsub-scanning-tool) that impersonates a DNS scanner but launches hidden PowerShell to fetch and decode a multi-layer, XOR-encrypted loader. The loader resolves encrypted payload locations from public dead drops (Pastebin, GitHub, YouTube, Instagram, Telegram, Google Docs), retrieves a password-protected .7z archive masquerading as Microsoft Photos, and deploys AsyncRAT/Quasar/Remcos-style RATs and Vidar infostealer. Pivoting from the module, Socket uncovered 222 GitHub repositories across 190 accounts using automated force-push workflows tied to a single email (ischhfd83@rambler.ru) to fake activity and credibility, some directly hosting Vidar, XMRig/BitMiner, and trojan loaders.
socket.devwriteupPublished and added 16 Jul 2026🛡️ Security Rapid7 MDR Team Discovers New SonicWall SMA1000 Zero Days Being Actively Exploited (CVE-2026-15409, CVE-2026-15410)
Rapid7's MDR team details active zero-day exploitation of SonicWall SMA1000 appliances via CVE-2026-15409 (unauthenticated SSRF in the /wsproxy websocket proxy, CVSS 10.0) chained with CVE-2026-15410 (local privilege escalation via path traversal in the ctrl-service remove_hotfix workflow) to achieve root RCE. The post includes a working Python exploit against the localhost Erlang service on port 1050 (using a hardcoded authentication cookie), an HTTP request PoC for the hotfix path-traversal chain, and extensive observed post-exploitation activity — credential/TOTP theft, VPN-less lateral movement to domain controllers via harvested LDAP service accounts — plus concrete log/IOC signatures and attacker-infrastructure IPs (FNS Holdings Limited ASN 206092) for hunting.
 rapid7.comwriteupAdded 10 Sep 2026, published 15 Jul 2026🛡️ Security
 Socket: Fake Braintree NuGet Package Skims Credit Cards
Socket's Threat Research team dissects Braintree.Net, a typosquatted NuGet package impersonating PayPal's official Braintree .NET SDK, which hooks credit card creation/transaction methods to exfiltrate PAN, CVV and merchant API keys (merchantId/publicKey/privateKey) to api.348672-shakepay[.]com. A companion package, DependencyInjector.Core, adds a .NET module-initializer-based harvester that unconditionally steals environment variables, appsettings.json/connection strings, and cloud/container metadata, and is also pulled in transitively by sibling typosquats SipNet and SipNet.OpenAI.Realtime. The writeup details the download-count inflation via 120 empty placeholder versions, production-only exfiltration gating, XOR-obfuscated C2 endpoint, and provides full IOCs, file hashes, and remediation steps.
socket.devwriteupPublished and added 15 Jul 2026🛡️ Security Socket: 11 Malicious NuGet Tools Pose as Game Cheats
Socket's Threat Research Team analyzed 11 malicious NuGet DotnetTool packages (published by account pepegit666) that impersonate game cheats/bots for titles like GTA5RP, Albion Online, and Throne and Liberty. Each package's .NET downloader resolves GitHub hosts via DNS-over-HTTPS, requests UAC elevation to resync the clock, and fetches a PyInstaller Windows payload (pepesoft.exe) from GitHub Releases/Hugging Face with dormant BitTorrent fallback code, that in turn authenticates to Google Sheets for telemetry, hardware-binds licenses, enforces a remote HWID ban-list, and, in three samples, drives Telegram bot commands that exfiltrate screenshots and modify Windows Installer registry keys on exit. The report includes full IOC lists (hashes, domains, hardcoded AWS-style keys, mutex GUID) and MITRE ATT&CK technique mappings.
socket.devwriteupPublished and added 15 Jul 2026🛡️ Security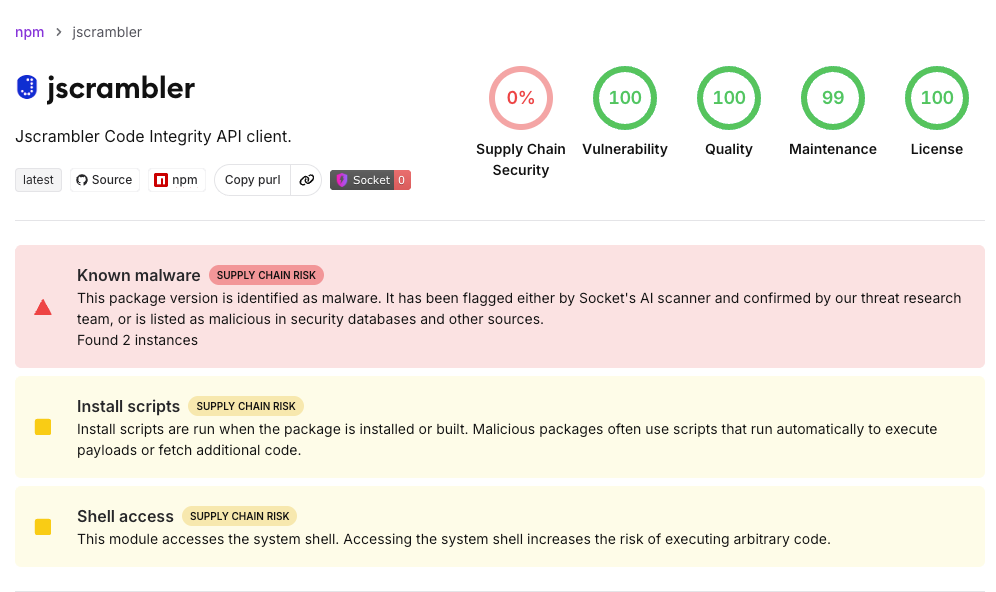 jscrambler npm Package Compromised in Supply Chain Attack
Socket's research team documents a supply chain compromise of the jscrambler npm package (v8.14.0+), where a stolen publishing credential was used to push malicious releases that drop platform-specific Rust-built infostealer binaries via a preinstall hook. The campaign evolved over the incident to evade scanners by moving the dropper from install scripts into a self-executing function inside index.js/CLI code (defeating --ignore-scripts), and the payload targets crypto wallets, cloud credentials (AWS/GCP/Azure), browser data, Discord/Slack/Telegram, and notably AI coding assistant configs (Claude Desktop, Cursor, Windsurf, VS Code) for MCP server credentials. Includes detailed RE of the ChaCha20-Poly1305 string-encryption scheme and full IOC hash list.
socket.devwriteupAdded 21 Sep 2026, published 11 Jul 2026🛡️ Security Socket: PolinRider
Socket's Threat Research Team documents the expansion of PolinRider, a North Korea-linked (Contagious Interview / Famous Chollima) supply chain campaign, finding 162 malicious release artifacts across 108 packages and extensions spanning npm, Packagist, Go modules, and Chrome extensions. Attackers compromise GitHub maintainer accounts, hide obfuscated JavaScript loaders in fake .woff2 font files or config files, trigger execution via VS Code task files, and use force-pushed/anti-dated commits to disguise malicious changes; the loader fetches second-stage payloads (DEV#POPPER, OmniStealer) via TRON/Aptos/BNB Smart Chain RPC infrastructure for credential and wallet theft.
socket.devwriteupPublished and added 2 Jul 2026🛡️ Security Socket: Chrome and Firefox VPN Extensions Add Clipboard Stealers via Malicious Updates
Socket's Threat Research Team analyzed "VPN Go: Free VPN" (Chrome Web Store, extension ID jgpfgonjjolillilkjfkiddakagkkpoj) and "Free VPN by VPN GO" (Firefox Add-ons), showing both shipped clean initial versions that later received malicious updates adding clipboard-monitoring "clipper" logic. The extensions poll the clipboard every 500ms (Chrome) or 1.5s (Firefox), chunk newly copied text, and exfiltrate it via GET requests to hardcoded IPs (178.236.252.133, 178.236.252.161, 77.91.123.187) at /html/continue.php, while real proxy/VPN functionality is retained as cover. The writeup includes deobfuscated code, version-by-version infrastructure changes, file hashes, bearer tokens, and MITRE ATT&CK technique mapping for defenders.
socket.devwriteupPublished and added 30 Jun 2026🛡️ Security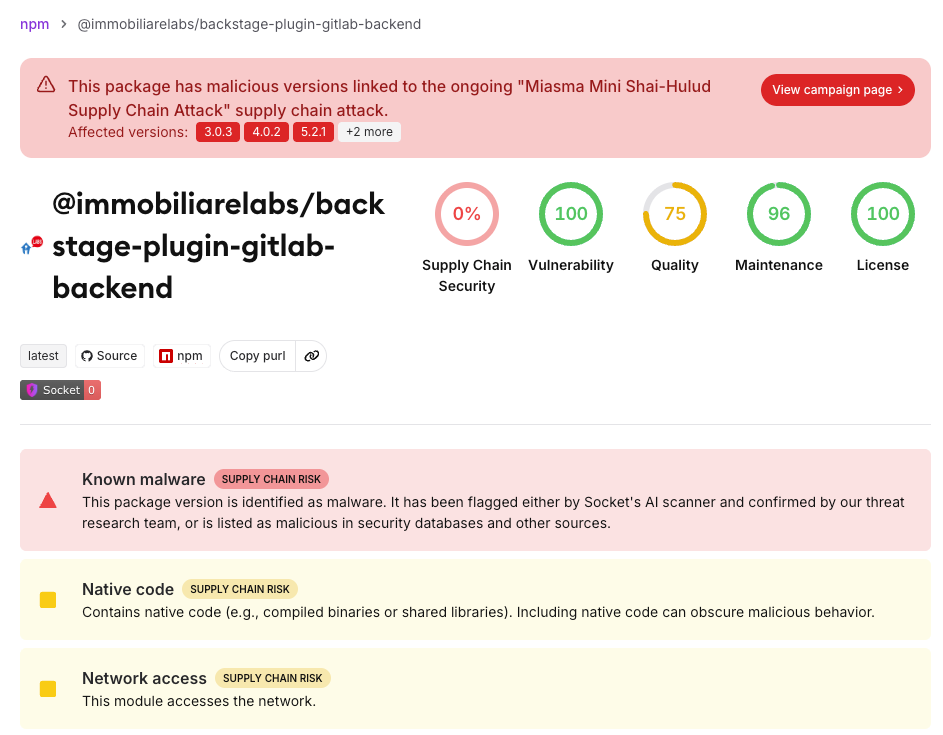 Socket: Miasma Mini Shai-Hulud Hits ImmobiliareLabs npm Packages
Socket Threat Research documents a new wave of the Miasma Mini Shai-Hulud npm supply-chain campaign compromising @immobiliarelabs Backstage plugins for GitLab integration and LDAP authentication, published on June 26, 2026. The malicious tarballs (e.g. @immobiliarelabs/backstage-plugin-gitlab@7.0.2) add a hidden root-level index.js triggered via the "Phantom Gyp" node-gyp binding.gyp trick, which decrypts an AES-128-GCM payload, bootstraps Bun, and steals npm/GitHub/cloud/SSH/CI-CD secrets while planting GitHub Actions and AI-IDE persistence. The report also traces a plausible root cause to the earlier compromise of codfish/semantic-release-action (tag-hijacking reported by StepSecurity) and highlights abuse of GitHub's deployment event trigger — a technique flagged by researcher Adnan Khan — to run attacker workflows without touching protected workflow files.
socket.devwriteupPublished and added 27 Jun 2026🛡️ Security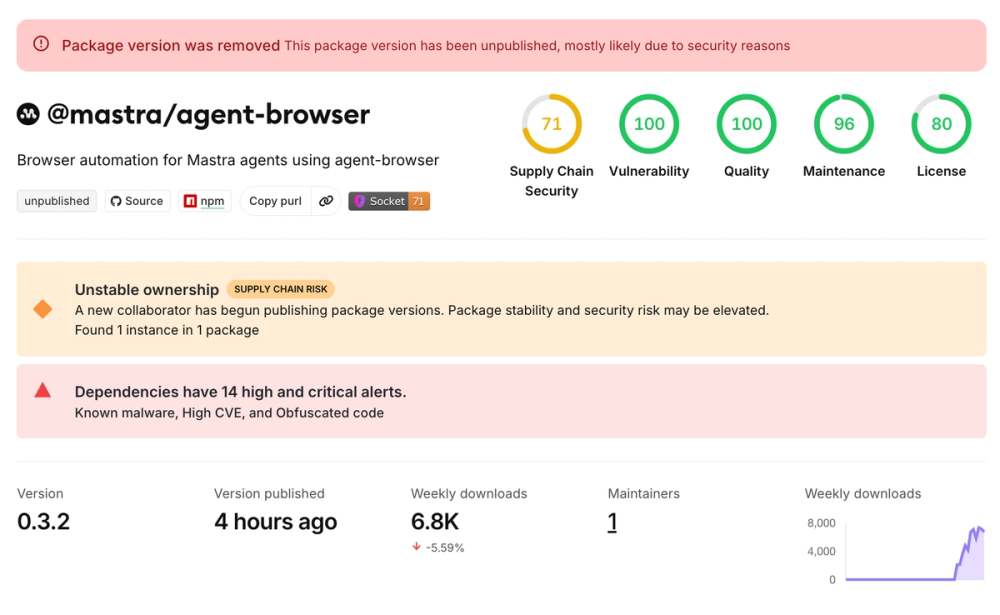 Socket: 141 Mastra npm Packages Compromised via Typosquatted Dependency
Socket's research team documents a supply chain attack in which npm account "ehindero" mass-published 141 malicious versions of @mastra/* packages (including @mastra/core, 918K weekly downloads) that were byte-identical to legitimate code but added a single new dependency: the typosquatted package easy-day-js. That package's postinstall hook (setup.cjs) disables TLS validation, fetches a second-stage cross-platform Node.js implant (protocal.cjs) that installs OS-specific persistence (Windows Run key, macOS LaunchAgent, Linux systemd unit disguised as Node/NVM tooling), inventories 166 cryptocurrency wallet browser extensions, steals Chrome/Edge/Brave history, and accepts arbitrary remote tasking (Node/Shell runners) from a hardcoded C2 over a custom ICAP-style protocol. The writeup includes full IOCs, SHA-256 hashes, and remediation guidance (rotate npm/CI/SSH credentials, treat affected hosts as compromised, disable install scripts).
socket.devwriteupPublished and added 20 Jun 2026🛡️ Security AutoJack: How a single page can RCE the host running your AI agent | Microsoft Security Blog
Microsoft Security Research disclosed "AutoJack," an exploit chain in AutoGen Studio (the prototyping UI for Microsoft's AutoGen multi-agent framework) where an agent with browsing capability (e.g., MultimodalWebSurfer) that renders an attacker-controlled webpage can be jacked into opening a WebSocket to the local MCP control plane at /api/mcp/ws. The chain combines three flaws: a localhost-only origin allowlist that the agent's own headless browser satisfies (CWE-1385), an auth middleware that explicitly skips /api/mcp/* paths without the intended WebSocket-level check (CWE-306), and a server_params query parameter that is base64-decoded into StdioServerParams and executed verbatim via stdio_client with no executable allowlist (CWE-78) — letting the page spawn calc.exe or arbitrary commands under the developer's account with no user interaction beyond the agent rendering the page. The issue was fixed pre-PyPI-release upstream (commit b047730) and never shipped in the published autogenstudio package; Microsoft provides mitigation guidance and Defender advanced hunting KQL queries to detect the pattern (suspicious child processes from autogenstudio, WebSocket calls carrying server_params, browser-automation processes reaching non-corporate domains).
microsoft.comwriteupAdded 20 Jun 2026, published 19 Jun 2026🛡️ Security Socket: npm Package Uses Prompt Injection + Token Flooding to Evade AI Malware Scanners
Socket Threat Research analyzed shai_hulululud@1.0.48596, a ~9.28MB npm package whose index.js opens with a Japanese-language block comment simulating bioweapon-production instructions to trigger LLM safety refusals, follows with a fake 'SYSTEM OVERRIDE' prompt-injection block aimed at AI reviewers, then floods the file with tens of thousands of repeated comment lines (3.5M+ tokens) before appending doubly-obfuscated (character-substitution plus AES) JavaScript. The deobfuscated payload reintroduces the same policy-triggering content and scanner/vendor-referencing strings, and was classified as protestware rather than a functional credential stealer; the piece argues this demonstrates a practical LLM-specific denial-of-service pattern (prompt injection + safety triggers + context flooding + obfuscation) that AI-assisted supply-chain scanners must defend against via deterministic preprocessing, fail-closed behavior, and combining LLM review with static/AST/entropy/behavioral analysis.
socket.devwriteupPublished and added 17 Jun 2026🛡️ Security Socket: GlassWASM
Socket's Threat Research team found two trojanized Open VSX extensions (ExarGD.vsblack, noellee-doc/flint-debug) that impersonate legitimate, verified VS Code Marketplace publishers to exploit a cross-registry trust gap. The extensions ship a TinyGo-compiled WebAssembly payload whose strings are ChaCha20-encrypted and only decrypted in memory at runtime; once running, it polls the Solana blockchain for SPL Memo instructions sent to an attacker wallet to resolve a rotating C2 host (dodod[.]lat) and then executes OS-specific download-and-execute commands via Node's child_process. Socket attributes the campaign with medium confidence to the GlassWorm developer and names this WASM-stager variant "GlassWASM," providing full hashes, wallet/memo IOCs, and detection guidance.
socket.devwriteupPublished and added 16 Jun 2026🛡️ Security- Anatomy of a Deno-Based Proxy & RAT
InfoGuard LABS DFIR analysis of an intrusion that combined mailbombing and Microsoft Teams IT-support impersonation to deliver a modular Deno-based RAT and network proxy. The malware splits functionality across four JavaScript files (app.js, back.js, helper.js, webui.js) that abuse Deno's permission model, use string-array-shifting obfuscation, communicate C2 over a CloudFront-fronted WebSocket, and expose loopback HTTP services for command execution (127.0.0.1:10021) and TCP tunneling/pivoting (127.0.0.1:10022). The post details persistence via the HKCU Run key, Teams impersonation telemetry (TeamsImpersonationDetected), and provides KQL hunting queries for Deno execution flags, CloudFront C2 traffic, and registry persistence.
dfir.chwriteupAdded 3 Sep 2026, published 15 Jun 2026🛡️ Security  Socket: 152 Chrome Live Wallpaper Extensions Hid Ad Tracking and Faked Google Search Traffic
Socket's Threat Research Team uncovered a family of 152 Chrome 'live wallpaper' new-tab extensions, built from one shared codebase and spread across 38 publisher accounts and three brand backends (tabplugins.com, yowgames.com, chromewallpaper.com), with ~105,000 combined installs. A 54-listing subset forges Google organic-search attribution via fake utm_source=google tags and a cloaked google.com/url uninstall redirect carrying spoofed ved/usg tokens, while every listing falsely claims 'no data collected' on the Chrome Web Store despite its own linked privacy policy admitting IP/ISP/click logging shared with AdSense, DoubleClick, and ad partners. All 141 verified samples also ship an undisclosed, inert IndexedDB enumerate-and-delete anti-forensic routine on every service-worker start.
socket.devwriteupPublished and added 13 Jun 2026🛡️ Security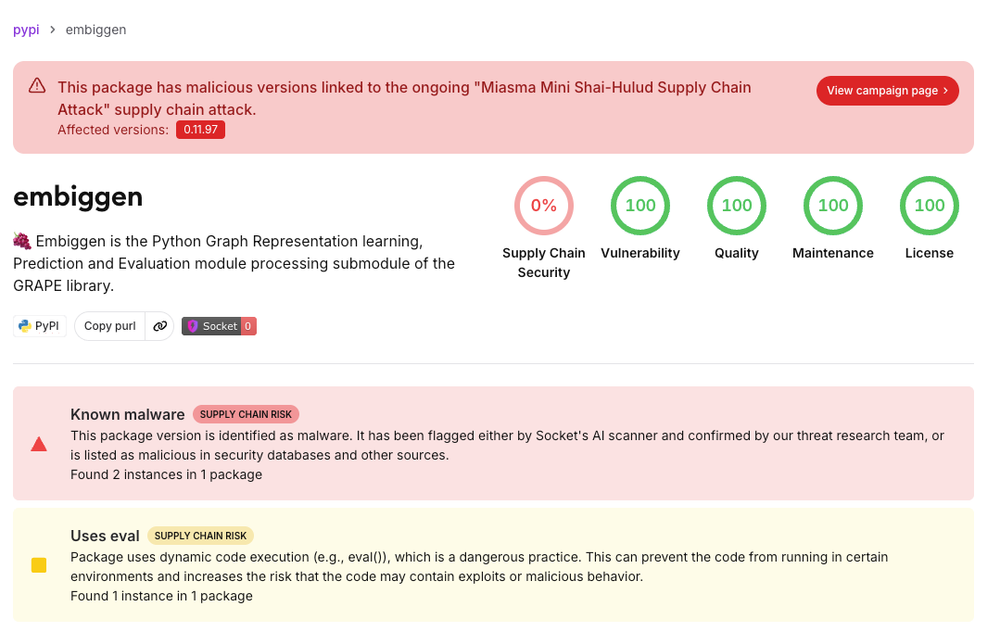 Miasma & Hades Worms
Socket's Threat Research team documents a new wave of 23 malicious PyPI artifacts (bioinformatics packages like embiggen/ensmallen/gpsea/pyphetools, typosquats like rsquests/tlask/rlask, and an MCP-themed langchain-core-mcp package) tied to the ongoing Mini Shai-Hulud/Miasma/Hades supply chain campaign. Unlike earlier .pth-hook wheels that bundled an obfuscated _index.js JavaScript stealer run via Bun, the bioinformatics cluster hides execution inside trojanized .abi3.so native extensions triggered at import time, while langchain-core-mcp ships only a .pth loader that scans sys.path for an external _index.js payload — a loader/payload split designed to evade detection rules. The payload also opens with a fake prompt-injection comment block meant to derail LLM-based static analysis tools before reaching the actual obfuscated stealer code that harvests GitHub, npm, PyPI, cloud, Kubernetes, SSH, and Docker credentials.
socket.devwriteupAdded 3 Sep 2026, published 10 Jun 2026🛡️ Security The sorry state of skill distribution
Trail of Bits researchers bypassed every agent-skill security scanner they tested — ClawHub's VirusTotal/Code Insight and GPT-5.5-based guard model, and skills.sh's Gen/Socket/Snyk-backed scanning, plus Cisco's skill-scanner — using techniques like context-truncation via 100,000 newlines, malicious payloads hidden inside .docx ZIP archives, Python .pyc bytecode poisoning to steal environment variables, and rhetorically-crafted prompt injection that convinced LLM analyzers a malicious npm/yarn registry change was benign. The piece also shows a legitimate Anthropic Office skill (soffice.py) using LD_PRELOAD in ways indistinguishable from malicious behavior, arguing static/LLM skill scanning is structurally unable to guarantee safety and that organizations should instead curate trusted skill marketplaces (e.g., trailofbits/skills-curated) rather than rely on public ones. PoC skills are published at trailofbits/overtly-malicious-skills.
 blog.trailofbits.comwriteupAdded 3 Sep 2026, published 3 Jun 2026🛡️ Security
 Socket: Famous Chollima Targets PHP Developers via Compromised Packagist Package
Socket researchers found malicious obfuscated JavaScript appended to a tailwind.js file inside a dev branch (dev-drewroberts/feature/test-case) of the legitimate Laravel package roberts/leads on Packagist. The payload uses TRON, Aptos, and BNB Smart Chain RPC services as a blockchain "dead drop" to fetch XOR-encrypted second-stage code, decrypt it, and execute it via eval() and a hidden detached Node.js child process, consistent with prior DEV#POPPER/OmniStealer/BeaverTail-family DPRK campaigns. The activity is attributed to Famous Chollima and resembles a Contagious Interview-style fake job/recruiter lure targeting PHP/Laravel developers, with full IOCs (wallets, XOR keys, hashes) and detection guidance provided.
socket.devwriteupPublished and added 1 Jun 2026🛡️ Security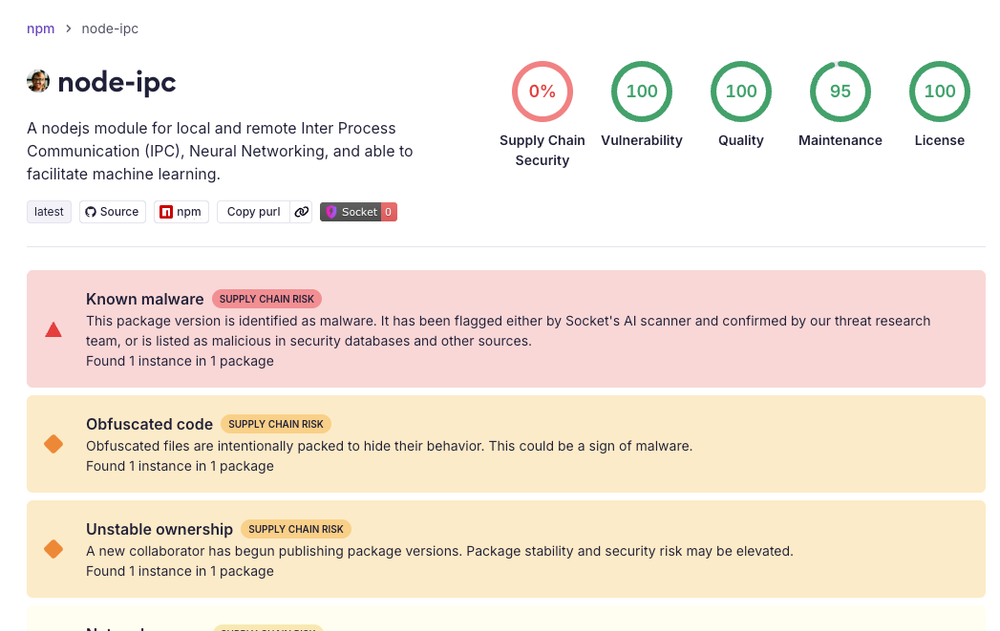 Socket: node-ipc npm Package Compromised
Socket's threat research team details a fresh compromise of the npm package node-ipc, where dormant maintainer account "atiertant" was hijacked via an expired recovery-email domain and used to publish three malicious versions (9.1.6, 9.2.3, 12.0.1) containing an obfuscated credential-stealing backdoor appended only to the CommonJS build. The payload forks a detached child process, harvests cloud/SSH/CI/database credentials and secrets from the filesystem and environment, archives them, and exfiltrates via covert DNS TXT queries to a typosquatted Azure-lookalike domain (sh.azurestaticprovider.net) and zone bt.node.js, with no observed C2 response handling or persistence. The write-up includes the full decode chain (XOR+HMAC+base64 obfuscation), dynamic validation, and complete IOCs (hashes, domains, temp file paths).
socket.devwriteupPublished and added 30 May 2026🛡️ Security


Showing 60 of 79
Show more