- Show HN: A language model that lives in a boot sector
bootgpt is a char-level language model that runs from a BIOS boot sector. A 512-byte hand-written asm MBR loads an 11.5 KB int8 model from 23 following sectors and runs it in 16-bit real mode on a 386, generating fake Linux dmesg boot logs. train.py quantises to int8 with power-of-two scales, and its integer simulation matches the asm output char for char.
 github.comrepoAdded 1 Nov 2026, published 31 Oct 2026🧠 AI
- llm-trails: What LLMs reach for inside a breached AWS account
llm-trails is an open study of what LLMs choose to do next inside a breached AWS account. It puts 14 models in 13 post-compromise situations, records only a single-turn plan with nothing executed, and codes each answer to CloudTrail events. The repo has the llmtrials harness, prompts, codebook, processed dataset (viz_data.json) and an interactive dashboard, so the study can be rerun or extended.
github.comrepoAdded 30 Oct 2026🧠 AI - rikugan: LLM reverse-engineering agent for IDA Pro and Binary Ninja
Rikugan is a reverse-engineering agent that runs inside IDA Pro and Binary Ninja. It has its own generator-based agent loop, context management, plan mode and 60+ tools, and does not depend on an external MCP server. An orchestrator spawns parallel subagents to analyze a binary. It supports Anthropic, Gemini, MiniMax, Kimi, OpenAI-compatible endpoints and Ollama, with per-model notes.
github.comrepoAdded 30 Oct 2026🧠 AI - rikugan: LLM reverse-engineering agent for IDA Pro and Binary Ninja
Rikugan is an open-source reverse-engineering agent that runs inside IDA Pro 9.0+ and Binary Ninja, with its own agent loop instead of an MCP server. It has 60+ tools (decompiler, xrefs, strings, types, IL/microcode), parallel subagent exploration, an experimental /modify natural-language patching command and an experimental Binary Ninja deobfuscation skill for control flow flattening and opaque predicates. It supports Claude, Gemini, MiniMax, Kimi, OpenAI-compatible endpoints and Ollama.
github.comrepoAdded 30 Oct 2026🛡️ Security - llm-trails: What LLMs reach for inside a breached AWS account
llm-trails is a research repo that placed 14 LLMs in 13 post-compromise AWS situations, asked only for their next move (single-turn, nothing executed), and coded each answer to CloudTrail events. It includes the llmtrials harness, prompts, codebook, processed dataset (viz_data.json) and an interactive dashboard. Rates are conditioned on the situation shown, and the aim is turning model behavior into detection priorities.
github.comrepoAdded 30 Oct 2026🛡️ Security - Show HN: I Turned DOOM into a Transformer
Doomformer compiles integer neural networks into ZDoom maps that run in ViZDoom. Voodoo dolls do the arithmetic, and sector light levels and plane heights hold the values. Python reads every value back and compares it with a NumPy integer reference at tolerance 0. It runs MNIST (97.16 % on all 10,000 digits, every pass exact), small transformers, a learning perceptron and a SUBLEQ machine. It is about 23,000 times slower than NumPy on a small MLP.
github.comrepoAdded 30 Oct 2026, published 29 Oct 2026🧠 AI - Show HN: Auto Dismiss Mac OS "Allow <app> to find devices on local networks?"
dontallow is a two-file Swift launchd agent for macOS 15 and later that clicks "Don't Allow" on the "find devices on local networks" prompt. It watches the UserNotificationCenter process through an Accessibility observer, supports pause and allowlist, and can decode the Local Network rule store to show orphaned rows. It explains why Chromium temp-bundle paths make the prompt recur, and gives a PPPC profile route for fleets.
github.comrepoAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security - Show HN: Overtone – Transcribe, correct and cut captions for any screen shape
Overtone is a caption format (.overtone.json), a CLI and a video.js plugin that store each spoken word once and cut captions separately per screen shape (16:9, 9:16 or custom). The transcribe pipeline combines gpt-transcribe, Azure AI Speech and optional ElevenLabs Scribe, resolves disagreements with an LLM vote, and uses an LLM editor for corrections. A small public benchmark reports 5.3% word error rate and $0.023–0.025 per audio minute.
github.comrepoAdded 30 Oct 2026, published 29 Oct 2026🧠 AI - Show HN: Hob - Open-source, on device alternative to Claude Cowork and ChatGPT
Hob is an MIT-licensed desktop app from Frigade that runs open-weight models such as Gemma and gpt-oss locally on Mac, Windows and Linux. It picks the best open-weight model that fits the user's computer and sets it up. It is positioned as a free, private, offline alternative to Claude and ChatGPT for tasks like filling out PDFs and working through documents. The page gives no technical detail on its runtime.
github.comrepoAdded 27 Oct 2026, published 26 Oct 2026🧠 AI - Show HN: Farol – A risk map of a pull request for the person who approves it
farol is a free, MIT-licensed CLI and GitHub Action that runs after an AI code review and gives the human approver a risk verdict (fast track, quick review, careful review) and a 0-100 score for a pull request. It uses the TypeScript type checker, go/types and Python ast to trace which pages, APIs and jobs a change reaches, and it adds diff coverage, security findings and contract breaks. It never executes or sends code.
github.comrepoAdded 26 Oct 2026, published 25 Oct 2026🧠 AI - alirezarezvani/claude-skills
claude-skills is an MIT-licensed library of about 398 Claude Code skills, agents, personas and plugins across 20 domains, including engineering, marketing, compliance and C-level advisory. Each skill is a SKILL.md with stdlib-only Python CLI tools and reference docs. Install scripts and convert.sh adapt it to Codex, Gemini CLI, Cursor, Aider, Windsurf and other coding agents, and it includes a skill-security-auditor scanner.
github.comrepoAdded 25 Oct 2026🧠 AI - alirezarezvani/claude-skills
claude-skills is an open-source MIT library of about 398 Claude Code skills, agents and plugins that also installs into Codex, Gemini CLI, Cursor and 9 other coding agents. The security-relevant parts are skill-security-auditor, a stdlib-only Python scanner that checks skills for command injection, data exfiltration, prompt injection and dependency supply-chain risks before install, plus a security-guidance PreToolUse hook, a security suite and compliance skills (ISO 27001, SOC 2, GDPR).
github.comrepoAdded 25 Oct 2026🛡️ Security  affaan-m/ECC | RepoDir
ECC (affaan-m/ECC) is an open-source performance optimization system for AI coding agents. It packages 261+ skills, 64+ agents and 84+ commands that tune Claude Code, Codex, Cursor and other agent harnesses for speed, memory and security. Practitioners can use it as a ready-made skills and harness configuration set. The RepoDir page gives only this short description, with no install steps or benchmarks.
 repodir.comrepoAdded 24 Oct 2026🧠 AI
- KhulekanisiyandaMchunu/llm-trading-arena
wtfibought (llm-trading-arena) is an MIT-licensed live arena where LLM agents trade virtual capital on real market data with all reasoning public. Users bring their own model and key, set the wake candle interval, leverage range and margin budget, with at most three symbols and twelve model calls per wake. The stack is Spring Boot on Java 25 with Spring AI, PostgreSQL, Redis and a React 19 frontend.
github.comrepoAdded 26 Oct 2026, published 23 Oct 2026🧠 AI - x86rc/unthemidator
Unthemidator is an automated unpacker for binaries protected with Themida, Code Virtualizer and WinLicense (v3.0 to v3.2.6.0, experimental v4.0). It works without executing the target, handles x86 and x64 exe, dll and sys files, decrypts imports, restores the IAT, rebuilds the PE and identifies VM versions and entry points. It does not devirtualize or unmutate code. Releases cover Windows x64 and macOS Apple Silicon.
github.comrepoAdded 27 Oct 2026, published 23 Oct 2026🛡️ Security - Spectrmachina/Ztrust
ZTrust is a Python supply-chain scanner that checks manifests, lockfiles, source and GitHub workflows for vulnerable or malicious dependencies (via OSV.dev), typosquats, leaked secrets, unsafe lockfiles and risky CI patterns such as pwn requests and script injection. It outputs console, JSON and SARIF 2.1.0 and ships as a GitHub Action. It also includes a FastAPI bounty service using commit-reveal and shielded Zcash payouts for researchers.
github.comrepoAdded 27 Oct 2026, published 22 Oct 2026🛡️ Security - SnailSploit/Claude-Red
claude-red is an MIT-licensed library of offensive security skills for the Claude Skills system, planned at about 130 skills across 23+ categories (web, Active Directory, cloud, exploit development, EDR evasion and others). Each skill is a SKILL.md file that loads on conversational triggers, so unused skills cost no context. It installs by git clone, sparse checkout per category, install.sh or pasting into a system prompt.
github.comrepoAdded 22 Oct 2026🧠 AI - SnailSploit/Claude-Red
claude-red is a library of offensive security skills for the Claude Skills system, each a SKILL.md file that loads on conversational triggers (for example, mentioning SQL injection loads offensive-sqli). Categories include web, Active Directory, cloud, mobile, exploit development, fuzzing, privilege escalation, post-exploitation and AI. It targets about 130 skills across 23+ categories, with an install script and sparse-checkout install per category. Built on Sahar Shlichov's offensive checklists, MIT licensed.
github.comrepoAdded 22 Oct 2026🛡️ Security - Sadra Majidi (@SadraMajidi04) on X
Impeccable is an open-source skill for AI coding agents that steers them away from generic UI output such as purple gradients and nested cards. It provides 24 commands (critique, audit, polish, typeset) and 61 detector rules that run without an LLM. It works with Claude Code, Cursor and Codex, and the repo is pbakaus/impeccable on GitHub. The source is a short tweet and gives no further detail.
 x.comrepoAdded 23 Oct 2026, published 22 Oct 2026🧠 AI
- Show HN: OnKey – I'm a bad singer, so I built an app to show where I'm off-key
OnKey is a free, MIT-licensed singing trainer for Apple Silicon Macs. After a song ends in Spotify, Apple Music or browser YouTube, it separates the lead vocal with UVR's MDX-Net Karaoke 2, tracks pitch with CREPE and turns it into syllable-level notes with the GAME model. On later plays it scrolls the notes, draws the user's live pitch and scores each line. Analysis runs on-device, and the repo explains the build steps and network requests.
github.comrepoAdded 24 Oct 2026, published 22 Oct 2026🧠 AI - OpenAI CLI
OpenAI CLI is OpenAI's official Go command-line client for the REST API. It lets users generate images, upload and download files, create and wait on batches, call the Responses API, and query admin usage endpoints from a terminal or shell script. It supports JSON, JSONL and YAML output, GJSON transforms, shell completion, and install via Homebrew, go install or release binaries.
github.comrepoAdded 23 Oct 2026, published 22 Oct 2026🧠 AI - Dan Kornas (@DanKornas) on X
aula-mcp is an open-source (MIT) TypeScript MCP server that connects an AI client to Denmark's Aula school platform. It exposes tools for profiles, calendar events, messages, notifications, posts and weekly plans. MitID credentials and OAuth tokens are stored in macOS Keychain or an AES-256-GCM encrypted file. The HTTP server binds to 127.0.0.1, and the presence write tool stays off until AULA_MCP_WRITE=1 is set.
x.comrepoAdded 23 Oct 2026, published 22 Oct 2026🧠 AI - Show HN: Omnara – Open-source alternative to Claude Managed Agents
Omnara is an open-source, self-hostable managed agent platform, an alternative to Claude Managed Agents and OpenAI's Agents API. It runs agents on any model (OpenAI, Anthropic, OpenRouter, Bedrock, LiteLLM, Ollama) and any machine, with Postgres-backed durable state, stateless workers, per-tool permissions, MCP, skills, memory, subagents, schedules and Slack, Discord and GitHub triggers. It ships a REST API, TypeScript SDK, CLI and Docker Compose setup.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🧠 AI - Cyber Detective💙💛 (@cyb_detective) on X
Python Cybersecurity Libraries is a curated GitHub list by Yogsec, shared in a post by cyb_detective. It groups Python libraries by task: network analysis, penetration testing, threat intelligence, reverse engineering and malware analysis, forensics and investigation, web application security, CTF, and machine learning for security. The tweet shows only the category names, not the individual libraries.
x.comrepoAdded 24 Oct 2026, published 21 Oct 2026🛡️ Security - eness/php2shell-CVE-2026-109618-CVE-2026-109619-PoC
php2shell is the name given to two critical pre-auth remote code execution flaws, CVE-2026-109618 and CVE-2026-109619, in PHP core's session upload progress handler (php_session_rfc1867_callback), where zend_hash_update frees live zval pointers that are later reclaimed and redirected into zend_call_function to run zif_system. This repository ships poc_109618.py, a fully automated four-stage HTTP exploit that leaks ASLR offsets via Set-Cookie headers against php:8.4.26-apache on Debian Bookworm, along with a root-cause C source patch, mitigation scripts to disable session.upload_progress, and WAF/ModSecurity/Lighttpd/Apache rules plus detection guidance for anomalous PHP worker child processes. Confirmed PHP versions include 8.4.4 and 8.2.34, with EOL branches (5.x, 7.x, 8.0, 8.1) left without official vendor patches.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security - ikow/php2shell-poc
php2shell-poc is a proof-of-concept and detection toolkit for CVE-2026-109618 and CVE-2026-109619, two PHP vulnerabilities tied to session.upload_progress handling and a Zend engine out-of-memory bailout path affecting PHP 5.4.0 through 8.5.11. The repository includes three working exploit chains, a Docker-based lab (PHP-FPM, nginx, Apache mod_php) for reproduction, and pre-built Suricata, Sigma, ModSecurity, and Lua detection rules. The author recommends disabling session.upload_progress as an interim mitigation, noting the underlying memory corruption requires a full PHP patch to fix.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security - vxcontrol/pentagi
PentAGI is an open-source, self-hosted multi-agent system that uses LLM agents to carry out penetration testing tasks autonomously. The MIT-licensed repo has a Go backend, a React frontend and GraphQL. It ships Docker Compose files for Langfuse tracing, Graphiti knowledge-graph memory and an observability stack. Topics list OpenAI and Anthropic as model backends.
github.comrepoAdded 20 Oct 2026🧠 AI - Show HN: VoidAccess – open-source dark web OSINT, from query to a graph
VoidAccess is a self-hosted, MIT-licensed dark web OSINT platform that runs a 13-step pipeline from a research query to a relationship graph. It collects from Tor indexes, paste sites, code forges, security feeds and .onion seeds, applies content-safety filters, and exports STIX 2.1, MISP, Sigma, YARA, Snort, Suricata, CSV and JSON. It runs as a CLI with SQLite or as a Docker Compose stack with PostgreSQL, FastAPI and Next.js.
github.comrepoAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security - ☣ KitPloit - Hacker Tools (@KitPloit) on X
DidierStevensSuite is a collection of Python scripts for malware analysis, file format parsing, hashing and forensic triage. It includes utilities for analysing PDF and OLE documents and for XOR-obfuscated data. The post is a short KitPloit announcement that links to the repository and gives no usage detail.
x.comrepoAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security - DeepInfer: High-performance inference framework for DeepSeek models
DeepInfer is DeepSeek's open-source inference framework for offline inference of DeepSeek-V4.1-Flash, released under Apache 2.0. It covers attention data parallelism, MoE expert parallelism with load balancing, draft-token decoding with confidence-scheduled verification, batch-invariant inference, deterministic sampling and structured outputs. It runs on NVIDIA SM100 GPUs and Huawei Ascend 950 NPUs. The KV cache system, prefill/decode disaggregation and load balancing are not included.
github.comrepoAdded 21 Oct 2026, published 20 Oct 2026🧠 AI - better-isms/grcskills
grcskills is a library of 60 plain SKILL.md files in the Agent Skills format, each describing how an experienced practitioner does one piece of governance, risk and compliance work. Examples are scope statements, risk registers, audit prep, vendor review and incident handling. Every skill names where the agent must stop and hand the decision to a person. Installs are pinned to reviewed release tags and checked by a validator.
github.comrepoAdded 20 Oct 2026🧠 AI - better-isms/grcskills
grcskills is an MIT-licensed library of 60 SKILL.md files (Agent Skills format) that let coding agents draft and prepare governance, risk and compliance work: scope statements, statements of applicability, risk registers, audit prep, vendor review, policies, privacy, incidents and continuity. Each skill names where the agent must stop so a person decides. Installs are pinned to release tag v2026.10.19.2, and a validator rejects network commands and credential paths.
github.comrepoAdded 20 Oct 2026🛡️ Security - Panos Gkatziroulis 🦄 (@ipurple) on X
Malvex (JoasASantos/Malvex) is an AI-driven malware analysis framework that integrates more than 30 analysis tools, a web REPL and an MCP server. Panos Gkatziroulis shared it on 19 October 2026 and noted that it was written by AI. The tweet gives no detail on which tools are bundled or how the AI drives them.
x.comrepoAdded 22 Oct 2026, published 19 Oct 2026🛡️ Security  Abhinav Singwal (@yogsec) on X
GetSubDomains is an open-source tool by yogsec that enumerates subdomains by querying crt.sh certificate transparency logs. It is aimed at the reconnaissance step of penetration tests and bug bounty work. The source is a short tweet pointing to a GitHub repository, so usage details and options are not given.
x.comrepoAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security- Saylor (@Kev96790724) on X
G-Krusch is an MIT-licensed, local-first Google Workspace hub built on Node.js 22 and SQLite WAL. It runs a 12-tool MCP server (SSE and Stdio) plus a REST bridge on port 5446 for Drive, Calendar and Gmail. It includes a 1,024-dimension hybrid Drive RAG with an embedding cascade (Ollama bge-large, then Gemini, then offline fallback) and FTS5 BM25. PDF extraction returns page citations. Tokens are kept in an AES-256-GCM vault; 30 of 30 tests pass.
x.comrepoAdded 21 Oct 2026, published 19 Oct 2026🧠 AI - Show HN: WhatsApp MCP running free on Cloudflare
whatsapp-mcp is an MCP server that runs in the user's own Cloudflare account and lets MCP clients such as Claude Code and Claude Desktop search and read WhatsApp chats. It links as a WhatsApp Web-style device through Baileys, stores messages in SQLite with FTS5 inside a Durable Object, and is read-only. The README documents deployment, OAuth sign-in, contact naming through agents, and workerd shims for Baileys.
github.comrepoAdded 20 Oct 2026, published 18 Oct 2026🧠 AI - eliasbiondo/antirion
Antirion is an open-source AI gateway shipped as one Rust binary with a built-in admin console. It sits between apps and providers such as OpenAI, Anthropic, Bedrock, Vertex and vLLM, translating between OpenAI, Anthropic, Gemini and Bedrock dialects. It covers routing with fallbacks and circuit breakers, budgets, guardrails, caching, MCP and A2A gateways, SSO, and a benchmark against Bifrost 2.2.4 and LiteLLM 1.103.1.
github.comrepoAdded 21 Oct 2026, published 17 Oct 2026🧠 AI - ralphtradesz/trading-hub
Trading Hub is a free macOS desktop trading platform built with C#/.NET 10 and Avalonia. It uses the user's Claude Code subscription: a chat writes and fixes C# strategies, an in-app MCP server lets Claude run backtests, optimizations and walk-forwards and write reports, and a risk agent proposes position sizes. Install and a Windows port are both driven by Claude Code prompts. License is MIT with Commons Clause.
github.comrepoAdded 19 Oct 2026, published 17 Oct 2026🧠 AI - DietrichGebert/ponytail
Ponytail is a single skill prompt (skills/ponytail/SKILL.md, with a compact AGENTS.md) that makes coding agents write only the code a task needs, reusing existing components while keeping validation, error handling, security and accessibility. The author benchmarked it in Claude Code with Opus 5.5 over 39 tasks, 5 runs each, including a real FastAPI + React repo. They report -53% code, -41% time, -26% cost and -45% tokens, and 98% of risky logic shipping with a test versus 68% without. It adds /ponytail-review and /ponytail-audit commands, a Claude Code cost/token band with a local board, and installs through Claude Code and Codex plugin marketplaces or as a rules file for Cursor, Copilot, Gemini, OpenCode and others.
github.comrepoAdded 17 Oct 2026🧠 AI - OWASP/MCP-Security-Testing-Guide
OWASP MCP Security Testing Guide is a living, GPL-3.0 collection treating the Model Context Protocol as a security boundary from user through model, MCP client, MCP server and tool to the target system. It covers threats, secure development, host/client controls, supply chain, enterprise gateways, detection, incident response, taxonomy, public incidents, case studies and review checklists, with 79 tests in Chapter 3 (sections 3.1–3.19). It includes a finding template, and it links the MCP Goat lab for safe practice. It is useful to AppSec, red team and SOC people assessing MCP deployments.
github.comrepoAdded 17 Oct 2026🛡️ Security - alex09x/kyb
KYB (Know Your Business) is a Rust/axum server that stores agent-written knowledge, incident reports and tasks as Markdown files in Git, one commit per change. Search is hybrid: Tantivy BM25 fused by reciprocal rank with local multilingual-e5-small ONNX vectors, and it can query historical versions or "as of" a date. It ships a kyb CLI, a native MCP endpoint (Claude Code, Codex, Antigravity, Gemini CLI), an installable agent skill, token auth with per-write attribution trailers, secret scanning on writes, and a web console. It targets persistent shared operational memory for multi-agent, multi-machine fleets.
github.comrepoAdded 17 Oct 2026🧠 AI - enisaeu/enisa-sbd-playbook
ENISA repository of 22 Secure by Design and Secure by Default playbooks for SMEs building products with digital elements. Each playbook has a principle, objective, checklist, minimum evidence and release gate, covering design, build, deployment, maintenance and decommissioning. It supports progressive adoption and CRA readiness without replacing legal obligations.
github.comrepoAdded 17 Oct 2026🛡️ Security - AikidoSec/safe-chain
Aikido Safe Chain is an open-source local proxy and shell-alias wrapper for npm, yarn, pnpm, bun, pip, uv, poetry, pipx and pdm. It checks every package download, including deep dependencies, against the Aikido Intel malware feed and blocks malicious packages before install. It also enforces a configurable 48-hour minimum package age by suppressing too-new versions in registry metadata. It supports custom registries and a self-hosted malware-list mirror, and has CI/CD install recipes for GitHub Actions, Azure Pipelines, CircleCI, Jenkins, Bitbucket and GitLab.
github.comrepoAdded 17 Oct 2026🛡️ Security  DeepSeek-v4.1-Flash-1017
Model card for DeepSeek-V4.1-Flash-1017, a minor update to DeepSeek-V4.1-Flash with MIT-licensed weights. It claims gains in reasoning, coding, agentic tasks and visual benchmarks, with shorter task time and output length that move the performance–cost Pareto frontier across agent harnesses (Claude Code for Terminal-Bench 4.0, Mini-SWE-V2 for DeepSWE v1.1). It ships no Jinja chat template. It provides a reference encoding.py for multi-turn chat, tool calling, thinking mode, numeric reasoning effort and interleaved images, plus deepseek-recipe, Rust libraries with Python bindings for prompt encoding and output parsing. Serving recipes are given for Transformers, vLLM, SGLang and Docker Model Runner.
 huggingface.corepoAdded 18 Oct 2026, published 17 Oct 2026🧠 AI
 Meta Muse Spark Open (816B-A42B) open-weights model card
Model card for Meta Superintelligence Labs' Muse Spark Open, an open-weights, natively multimodal model with 816B total and 42B active parameters and a 1M-token context window. It targets coding and agentic work (tool use, long-horizon tasks, multimodal reasoning, synthetic data generation, LLM-as-judge). It ships in BF16 and NVFP4, needs about 700GB VRAM (NVFP4) or 2TB (BF16), runs on SGLang, vLLM, Transformers, TensorRT-LLM, Unsloth, llama.cpp and MLX, and supports a reasoning_effort setting. The Muse Model License requires "Built with Muse Spark Open" attribution and a separate agreement for Model-as-a-Service above $20M revenue. The card reports safety results against Kimi K3 on cyber, chem/bio and loss-of-control evals.
huggingface.corepoAdded 17 Oct 2026🧠 AI- Llama.cpp on a jailbroken PS5: run any GGUF model natively on the console
PS5LM is a homebrew app for jailbroken PS5s (firmware 7.00–13.60). It runs llama.cpp with the ggml-vulkan backend on the console's RDNA 2 GPU, using 11.4 GB of shared memory, and loads any GGUF model. It serves OpenAI /v1/chat/completions, Anthropic /v1/messages (usable from Claude Code, Codex and opencode) and a browser chat page on port 8081. It also supports image-projector vision models and TypeSafe-style decision models through a /v1/systemone endpoint. A planner picks the longest context and best cache that fit the free memory, and the app downloads models from Hugging Face.
github.comrepoAdded 17 Oct 2026, published 16 Oct 2026🧠 AI - OpenMOSS/MOSS-Image
MOSS-Image is an open-source text-to-image model family from OpenMOSS with a 5B backbone, released October 2026 as MOSS-Image-Base and MOSS-Image-SFT. It supports JSON layout control with bounding boxes, text rendering inside images, and prompts up to 4K tokens. The repo gives a Diffusers pipeline, a Gradio app, a ComfyUI plugin, LoRA training guidance, a prompt-enhancer skill and day-0 SGLang and vLLM-Omni support.
github.comrepoAdded 20 Oct 2026, published 16 Oct 2026🧠 AI - gichirimaku/wp2shell-PoC
wp2shell-PoC is a Python proof-of-concept exploiting a pre-authentication RCE chain in WordPress core, combining CVE-2026-63030 (REST API batch route confusion) and CVE-2026-60137 (SQL injection in WP_Query). It demonstrates escalation from the route-desync bug through blind SQLi, customize_changeset forgery, and hook re-entry to administrator account creation and arbitrary command execution via a malicious plugin upload. The tool supports vulnerability checking, data extraction (union, error-based, blind techniques), and full shell access with or without existing admin credentials.
github.comrepoAdded 23 Oct 2026, published 15 Oct 2026🛡️ Security - Show HN: Graphicle, a Rust port of Graphify with memory for coding agents
Graphicle is a local-first Rust program that parses a repository into a tree-sitter code graph (a port of Graphify) and adds project memory: docs, reviewed decisions and captured Claude Code/Codex sessions. It serves cited file-and-line excerpts within a token budget via one MCP server, CLI and browser app, backed by a single SQLite file, with no API key or telemetry. The README reports a code-only extract on Kubernetes (31k files) in 3m18s versus 26m38s for Graphify 0.9.88, and a memory comparison against seven systems. Agent-proposed memories need user approval and go stale when the code they reference changes.
github.comrepoPublished and added 14 Oct 2026🧠 AI - morluto/rea
REA (rea-agents on npm) registers an MCP server and matching workflow instructions with coding agents such as Claude Code, Codex, Cursor and Gemini CLI. It exposes tools for inspecting native binaries through Hopper, Ghidra or IDA (with optional objdump and Rizin), JavaScript/Electron apps and ASAR archives, .NET assemblies and websites. Results come back with evidence and limitations, so the agent can explain how a feature works and write and test its own implementation. Analysis runs locally, there is a CLI with the same workflows, and the showcases include C reconstructions verified against original x86 function bytes.
github.comrepoAdded 14 Oct 2026🧠 AI - morluto/rea
REA (rea-agents) is an MIT-licensed toolkit that exposes native-binary, JavaScript/Electron, .NET assembly and website analysis to AI agents via MCP, and also as a local CLI. It drives Hopper, Ghidra, IDA, objdump or Rizin for disassembly and pseudocode, recovers modules and Electron IPC boundaries from ASAR/JS apps, and returns findings with evidence and limitations. Showcases include reconstructing a x86 audio helper into byte-matching C and tracing an Electron clipboard API through preload and IPC; the README also carries lawful-use and licensing guidance.
github.comrepoAdded 14 Oct 2026🛡️ Security - BijectiveLabs/trading-research-agents
Open-source Python CLI (`tra`) for autonomous trading desks in which LLM analysts (technical, macro, on-chain, sentiment) and validators only give opinions on figures the system computed. Fixed rules do the arithmetic: pricing the round-trip cost, applying risk limits, sizing, cost gates, and sending a single order with stop attached via ccxt (Bybit and OKX demo accounts tested). It supports multiple model providers with per-role models, effort settings and fallbacks. Every answer is parsed against a closed schema, every refusal is logged with the figure behind it, and models can tighten but never loosen controls. This makes it a concrete reference for keeping LLM agents away from arithmetic and money.
github.comrepoAdded 18 Oct 2026, published 13 Oct 2026🧠 AI - BijectiveLabs/bitra
bitra (CLI name tra) is an MIT-licensed Python framework from Bijective Labs for autonomous trading agents. Language models only read system-computed figures and give opinions, while deterministic code prices the round trip, applies declared limits, sizes the trade and sends one order with stop attached. Every cycle's briefs, answers and refusals are stored on disk with hashes. It supports many model providers and ccxt venues, with sandbox, demo and mainnet tiers.
github.comrepoAdded 25 Oct 2026, published 13 Oct 2026🧠 AI - santosomar/AI-agents-for-cybersecurity
Companion repository for Omar Santos's Pearson and O'Reilly trainings and books. It has eight parts of runnable Python labs: chat models, embeddings, prompt templates, LCEL prompt chaining, Chroma-based RAG, ReAct/LangGraph/CrewAI/DeepAgents agents, and FastMCP servers (nmap, CISA KEV, Shodan). It also includes guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz), a tokenomics module on agent cost (context compounding, prompt caching, model routing, token budget guards, batch API, cost per accepted outcome), and a vendor-neutral design spec for a human-gated multi-agent assessment harness. It is a current, practical curriculum for building and operating agents. Some examples act on real systems and should only be run in an authorized lab.
github.comrepoAdded 13 Oct 2026🧠 AI - santosomar/AI-agents-for-cybersecurity
Omar Santos's companion repo for his Pearson/O'Reilly trainings and books, organised in eight parts. They cover LangChain prompts, chains and RAG (Chroma), and agents (LangGraph, CrewAI, DeepAgents). They also cover FastMCP security servers (nmap, CISA KEV, Shodan) and attack-surface-management and SOC agent examples. Later parts have security guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz) with hardening notes and 2026 CVE mapping, agent cost/tokenomics scripts including denial-of-wallet budget guards, and a vendor-neutral spec for a human-gated multi-agent security-assessment harness (scope manifest, approval gates, kill switch). Useful as a hands-on path into AI-agent security tooling, with warnings that some examples act on real systems.
github.comrepoAdded 13 Oct 2026🛡️ Security - Show HN: SolidCraft – Open-Source Parametric CAD in Rust (With MCP Support)
SolidCraft is an open-source parametric 3D CAD application written in pure Rust. It has constrained sketches with its own solver, a feature timeline, assemblies, sheet metal, and STEP/IGES/3MF/STL export. It runs on desktop (egui+wgpu), in the browser, and as a headless CLI. The built-in MCP server (`solidcraft-cli mcp`) gives agents tools such as execute, batch, inspect_design, measure, set_parameter, screenshot and export. They can model headless or drive the running app over a JSON-lines control channel. A rover with 3,323 timeline steps was built entirely through MCP, which shows agent-driven parametric modelling working at scale.
github.comrepoPublished and added 13 Oct 2026🧠 AI  google/embeddinggemma-2
Model card for EmbeddingGemma 2, an open (Apache 2.0) 740M-parameter multimodal embedding model from Google DeepMind built on Gemma 4. It maps text, code, images, video and audio into one 768-d space, with a 270M text backbone and optionally loadable 170M vision and 300M audio encoders, an 8K context, and Matryoshka truncation to 128/256/512/768 dims. The card gives practical guidance: task instruction prefixes, re-normalising after truncation, avoiding float16 (NaN or degraded embeddings), interleaved multimodal inputs with placeholder tokens, and vision token budgets. It targets on-device search, RAG, classification and clustering.
huggingface.corepoAdded 12 Oct 2026🧠 AI- Show HN: Atticus – Hold-to-talk voice assistant for macOS that runs on Claude -p
Atticus is an MIT-licensed macOS 26+ hold-to-talk voice assistant that uses Apple's on-device speech transcription and runs AI requests through Claude Code on an existing Claude Pro/Max plan, so no API key is needed. Simple commands skip the model entirely (apps open in 0.08 s), actions it has seen once are learned as zero-cost shortcuts, and a "remember…" memory persists across asks. It also sets up no-AI background watchers (polling every 5 s) and holds itself to a budget of a median under $0.002 and 6 s per AI ask, with a system prompt under 10,000 characters.
github.comrepoPublished and added 12 Oct 2026🧠 AI - zero-lab-ai/skills
zero-lab-ai/skills is a collection of 56 portable SKILL.md agent skills in 10 installable plugins from zero-lab.ai. They cover authorized defensive assessment, penetration testing, red teaming, detection engineering, purple teaming and engagement operations. Skills install via the Claude marketplace layout or `npx skills add`, and a make check release gate runs linting and tests.
github.comrepoAdded 23 Oct 2026, published 11 Oct 2026🛡️ Security - sepehr071/iran-mcp
iran-mcp is an open-source catalog of 39 MCP servers (488 tools) that let AI agents query Iranian websites such as Digikala, Torob, Divar, Snappfood, Jabama, Paziresh24, TSETMC and qavanin.ir, with prices normalised to Toman. Most servers are unofficial, read-only Python packages run with uvx; three are official hosted servers. It ships Claude Code plugins, Agent Skills, bundles, proxy lists and a machine-readable servers.json.
github.comrepoAdded 24 Oct 2026, published 11 Oct 2026🧠 AI - Dan Kornas (@DanKornas) on X
Arcjet JS SDK is an Apache-2.0 JavaScript monorepo that adds runtime security checks to AI apps, agents and HTTP endpoints. It ships framework SDKs (Next.js, Node.js, Bun, Deno, Fastify, NestJS) plus a Guard API for agent tool calls, MCP handlers, queue workers and background jobs that have no HTTP request object. Features include prompt injection detection, sensitive-information detection (PII, credit cards, custom patterns) and token-bucket, fixed-window and sliding-window rate limiting.
x.comrepoPublished and added 11 Oct 2026🛡️ Security - Dan Kornas (@DanKornas) on X
Arcjet JS SDK is an open-source (Apache-2.0) JavaScript monorepo that adds runtime security to AI apps, agents and HTTP endpoints. It ships request SDKs for Next.js, Node.js, Bun, Deno, Fastify and NestJS. It also has a Guard API for places with no HTTP request object, such as agent tool calls, MCP handlers, queue workers and background jobs. Built-in checks cover prompt-injection detection, sensitive-information detection (PII, credit cards, custom patterns) and token-bucket, fixed-window or sliding-window rate limits, including token budgets.
x.comrepoPublished and added 11 Oct 2026🧠 AI - sakidekin/CVE-2026-41940-PoC
This repository hosts a proof-of-concept for CVE-2026-41940, described as a CVSS 10.0 unauthenticated authentication bypass in cPanel and WHM caused by CRLF injection into server-side session files via the Authorization header. The accompanying Python tool (cve.py) can detect vulnerable cPanel/WHM instances, retrieve system and account information, and perform post-exploitation actions such as running OS commands, changing the root password, and opening an interactive WHM shell. It also supports bulk scanning workflows piped from subfinder, httpx, and Shodan.
github.comrepoAdded 23 Oct 2026, published 11 Oct 2026🛡️ Security - bilawalsidhu/gods-eye-view
God's Eye View is an open-source, vanilla JavaScript + CesiumJS + Vite 3D globe that fuses live public feeds (aircraft, ships, satellites, quakes, public cameras, weather) into one explorable scene. Its AI layer is a hands-free voice agent on the OpenAI Realtime API with 30 tools: camera fly-to, whiteboard annotations, analyst queries over live layers, and scene-context and screenshot grounding. Keys stay server-side and the browser gets only a short-lived session token. An experimental ChatGPT/Codex OAuth path is also supported. The app doubles as an MCP server, so Claude Desktop, Codex or ChatGPT can open the globe from a conversation.
github.comrepoAdded 11 Oct 2026🧠 AI - bilawalsidhu/gods-eye-view
God's Eye View is an open-source, vanilla-JavaScript CesiumJS and Vite client that puts live aircraft, ships, satellites (SGP4), earthquakes, fires, public CCTV and mapped ALPR cameras on one photorealistic 3D globe. It adds cockpit tracking, FLIR/NVG sensor shaders and a voice agent built on the OpenAI Realtime API. It works without API keys, and the docs cover server-side key brokering with SSRF protection, localhost binding and a SECURITY.md threat model. For OSINT/GEOINT practitioners it is a hackable base for fusing public signals, with an explicit rule against person-tracking features.
github.comrepoAdded 11 Oct 2026🛡️ Security - Talorys – A self-hosted personal AI agent on Cloudflare's free tier
Talorys is an open-source, single-user personal AI assistant deployed with one command (npx create-talorys) into the user's own Cloudflare account. It uses a Cloudflare Agents SDK Durable Object with SQLite for conversations, memories, tasks, notes and automations, Workers AI (@cf/zai-org/glm-4.7-flash) for streaming chat with tool calling, and Durable Object alarms for reminders and scheduled AI routines. It stays within the Workers Free plan, with a private Worker behind a Pages Function service binding, owner-password auth, per-day AI usage guardrails, and fallback to non-AI features when quota runs out.
github.comrepoPublished and added 10 Oct 2026🧠 AI - argoproj-labs/mcp-for-argocd
TypeScript MCP server for Argo CD that lets MCP clients (Cursor, VS Code, Claude Desktop) list, inspect, create, update, delete and sync applications, read logs and events, and run resource actions through natural language. It supports stdio and HTTP stream transports, with a stateless mode for multi-replica Kubernetes deployments. The security design is detailed: API tokens are read only from env vars or headers and never from tool arguments, the default token is bound to the default base URL, a per-host token registry covers extra instances, a read-only mode disables write tools, and the HTTP listener binds loopback by default and requires an inbound auth token if exposed.
github.comrepoAdded 10 Oct 2026🧠 AI  Qwen3.8-27B (Apache-2.0, multimodal dense, 262k ctx)
Model card for Qwen3.8-27B, a 27B dense vision-language model from the Qwen team with a hybrid Gated DeltaNet / Gated Attention layout (64 layers, 16×(3 DeltaNet + 1 attention)), MTP training, and 262k native context extensible to 1M via YaRN. It targets coding, research and long-horizon agentic tasks, with thinking on by default, reasoning_effort levels (xhigh/medium/low) and preserve_thinking. The card gives deployment recipes for Transformers, vLLM, SGLang and TokenSpeed, recommended sampling parameters, video-token settings for hour-scale video, and benchmark notes (SWE-bench Pro, NL2Repo-Bench, DeepSWE, HLE, MathVision, WebArena-Verified, etc.).
huggingface.corepoAdded 9 Oct 2026🧠 AI- morluto/awesome-reverse-engineering
awesome-reverse-engineering is a CC0 curated list of reverse-engineering tools and learning resources, organized by task: triage, native analysis, debuggers, instrumentation, deobfuscation, malware analysis, mobile, firmware, file formats, games, diffing, symbolic execution, lifting and AI agents. Each entry notes licensing, maintenance status and prerequisites. It also covers MCP integrations, CTF practice sites and related awesome lists.
github.comrepoAdded 27 Oct 2026, published 9 Oct 2026🛡️ Security - Show HN: Let your AI agents paint big arrows, boxes and text on your screen
bigarrow is an MIT-licensed, single-binary Swift macOS CLI that draws a click-through arrow and sign over all windows so an AI agent can show a human where to click, paste or act (permission prompts, 2FA, OAuth consent). It ships an Agent Skills package (installed via `bigarrow install-skill`) for Claude Code and Codex, with JSON output and exit codes, and can target by Accessibility label, coordinates, window or Peekaboo snapshot. The README documents the skill's token cost (182 tokens for the description, 1,398 for the instructions) and 104 automated tests.
github.comrepoPublished and added 9 Oct 2026🧠 AI - Show HN: Apogee: Rebuilding Mozilla's Orbit, fully local and private
Apogee is a privacy-first browser extension (Chrome/Firefox) that summarizes articles, YouTube/Bilibili videos, PDFs, DOCX and pasted text entirely on-device, inspired by Mozilla's discontinued Orbit. It runs models via WebGPU or WebAssembly in the browser, or connects over loopback to a local Ollama or llama.cpp server, with local passage retrieval for Q&A, grounded sentence highlighting, and Opus-MT translation. It shows a practical no-backend, no-API-key architecture for local LLM apps, with a Node.js extractor test harness for contributors.
github.comrepoPublished and added 9 Oct 2026🧠 AI - Show HN: Edi Life OS – self-hosted life dashboard with an MCP server for AI
Edi Life OS is a self-hosted dashboard (PHP 8.1+, MySQL, vanilla JavaScript) that combines focus timer, habits, goals, Kanban tasks, finances and notes in ten workspaces. It includes an optional Node.js MCP server that exposes 15 tools over stdio. The tools let Claude Desktop, Claude Code or Codex read the dashboard, create goals and tasks, log habits and record expenses. The MCP server calls only the app's bearer-token /api/v1 HTTP API and never touches the database or credentials. The README is candid about limits: the token has no scopes, there is no app-level rate limiting, and the secret-note flag is only a visibility setting, not encryption.
github.comrepoPublished and added 9 Oct 2026🧠 AI - mattpocock/skills — agent skills for engineers
mattpocock/skills is a collection of small, composable "agent skills" for software engineering that install into Claude Code, Codex, GitHub Copilot, Gemini CLI, Cursor, OpenCode, Devin, Windsurf, Amp and Pi via plugin managers or the `npx skills` CLI. It packages practices like interview-driven requirement gathering (/grill-me, /grill-with-docs), domain-model/glossary building, test-driven development with red-green-refactor (/tdd), bug diagnosis loops, codebase architecture improvement, ticket triage and spec-to-implementation workflows (/to-spec, /to-tickets, /implement, /implement-spec), splitting skills into user-invoked orchestrators and model-invoked reusable disciplines. It's built by Matt Pocock as an alternative to heavier process-owning frameworks like GSD, BMAD and Spec-Kit, aiming to keep engineers in control while giving coding agents better feedback loops and shared vocabulary.
github.comrepoAdded 8 Oct 2026🧠 AI  Aleph Alpha Kolibri-1 (78B MoE, Apache 2.0)
Kolibri-1 is Aleph Alpha's 78B-parameter mixture-of-experts reasoning model focused specifically on German and English, released under Apache 2.0 with weights, a vLLM plugin, and an extensive model card. It supports explicit reasoning-effort levels, Hermes-style tool calling, and a native 262144-token context validated to over 1M via sliding-window attention; the card details its UniBPE German-aware tokenizer, pre-training mid-training and long-context training recipe, MergeMix-based data-mix search, Merlin-Arthur hallucination-mitigation RL protocol, and benchmark results against Qwen3.5, Gemma 4, Nemotron 3 Nano, and Apertus on MMLU-Pro, GPQA, AIME, SWE-bench Verified, Terminal-Bench 2.1, and HLE.
huggingface.corepoAdded 8 Oct 2026🧠 AI- trhhubsd/ARTEX
ARTEX is an AGPL-3.0 autonomous penetration-testing system with a Go backend and Next.js frontend, backed by PostgreSQL. A planner agent and parallel worker agents share a global asset graph and a per-task exploration graph, with human-in-the-loop approval, a MITM traffic-recording proxy, ScopeSentry asset sync, vulnerability retesting and a shared todolist for multi-step attack chains. The README claims a Baidu agent+ attack-defense challenge win and limits use to local isolated labs.
github.comrepoAdded 27 Oct 2026, published 8 Oct 2026🛡️ Security - Dark Web Informer (@DarkWebInformer) on X
Infoooze is an open-source command-line OSINT reconnaissance toolkit (github.com/devxprite/infoooze) that consolidates common footprinting tasks into one CLI: username enumeration across platforms, email discovery, subdomain enumeration, port scanning, WHOIS/DNS lookups, IP/HTTP header analysis, EXIF metadata extraction, GitHub recon, and URL scanning/expansion. It automatically saves results, making it a lightweight all-in-one alternative to running several separate recon tools.
x.comrepoPublished and added 8 Oct 2026🛡️ Security - Sub-1-Bit LLM Compression via Latent Factorization
test
github.comrepoPublished and added 8 Oct 2026🧠 AI - microsoft/mxc
MXC is Microsoft's cross-platform sandboxed code execution system for running untrusted workloads — model output, plugins, and tool calls — behind a unified containment model with Rust, .NET, and Node SDKs. It offers multiple containment backends (ProcessContainer, Windows Sandbox, LXC, Bubblewrap, Seatbelt, MicroVM/Nanvix, Hyperlight, WSLC) with JSON-based filesystem, network, and UI policies, plus diagnostics like audit mode for building policies from observed access.
github.comrepoAdded 8 Oct 2026🧠 AI - microsoft/mxc
MXC is Microsoft's cross-platform sandboxed code execution system for running untrusted code such as LLM/agent output, plugins, and tools, offering containment backends ranging from OS-native process sandboxes (Windows Sandbox, LXC, Bubblewrap, Seatbelt) to full VMs (Nanvix MicroVM, Hyperlight). It exposes a unified JSON-based policy model for filesystem, network, and UI access controls, with Rust, .NET, and Node SDKs plus diagnostic tooling (audit mode, access-denied logging) to help developers tune containment rules for agentic workloads.
github.comrepoAdded 8 Oct 2026🛡️ Security - chainguard-dev/malcontent
malcontent is Chainguard's open-source malware/supply-chain discovery tool that analyzes binaries (ELF, Mach-O, PE, a.out) and scripting-language source across Linux, macOS and Windows using 14,500+ YARA rules (including third-party rules from Avast, Elastic, FireEye, Mandiant, Nextron and ReversingLabs). Its standout feature is differential analysis ("mal diff"), which compares two versions of a build artifact or OCI image against a known-good baseline to surface newly introduced risky behaviors — the technique the project demonstrates on the 3CX supply-chain compromise by flagging unexpected high-risk changes to libffmpeg. It also supports threshold-based scanning ("mal scan") and unfiltered capability enumeration ("mal analyze"), and is designed to run inside CI/CD pipelines, including air-gapped environments via embedded rules.
github.comrepoAdded 8 Oct 2026🛡️ Security - target/strelka
Strelka is Target's open-source, container-based real-time file scanning system for threat hunting, threat detection, and incident response, built in Go and Python. It runs 50+ scanners (YARA, PE parsing, encrypted ZIP cracking, entropy analysis, etc.) to extract metadata and content from files at enterprise scale, which can feed a SIEM for alerting on suspicious artifacts like an Emotet-laden encrypted ZIP payload.
github.comrepoAdded 8 Oct 2026🛡️ Security - deepfence/YaraHunter
YaraHunter is Deepfence's open-source scanner that applies YARA rulesets against container images, running Docker containers, and filesystems to detect indicators of compromise such as malware and cryptominers. It supports CI/CD build-time scanning, at-rest image scanning, and runtime container scanning, with JSON output for automation, and is designed to eventually integrate into the Deepfence ThreatMapper platform. The README walks through detecting the XMRig cryptominer inside a container image as a worked example.
github.comrepoAdded 8 Oct 2026🛡️ Security - Tracer-Cloud/opensre
OpenSRE is an open-source framework for building AI SRE agents that resolve production incidents by correlating logs, metrics, traces, deploys and runbooks across 60+ connected tools (observability, cloud infra, incident management, MCP). Beyond the agent runtime (CLI, Python API, Slack/PagerDuty/Telegram integrations), the project's stated mission is to build an RL training and evaluation environment — explicitly modeled on SWE-bench's role for coding agents — to scale realistic infrastructure-failure scenarios as a benchmark for AI SRE.
github.comrepoAdded 8 Oct 2026🧠 AI - Port of the TypeScript compiler, checker and lsp to Rust, by LLM
ts-rust (npm package tsc-rs) is a from-scratch Rust port of Microsoft's TypeScript compiler/checker/language server (typescript-go), produced almost entirely by LLM coding agents rather than hand-written. The author first spent over $400,000 in API tokens running GPT-5.6 Sol and GPT-6 Astra in long agentic '/goal' loops, which wrote 1.3M lines of Rust but plateaued at ~84% compatibility; switching to Claude Opus 5.5 produced a working version in 10 hours and, after ~$24,000 of further API spend over two weeks, reached 100% compatibility on tested real-world projects while passing all 181,711 ported Go baseline tests. Benchmarks show the Rust port running about 1.6x faster than the Go tsc 7 compiler (though slower than Bun's native `bun check`) across dozens of open-source codebases including VS Code, TanStack Query, Sentry and T3 Code.
github.comrepoPublished and added 8 Oct 2026🧠 AI - Show HN: NanoMuse – An open-source AI agent for your phone and computer
nanoMuse is an open-source personal AI agent that runs across phone, desktop, and web, built on an on-device sandbox (OpenMinis with proot/Alpine Linux on mobile) and the DeepSeek Harness on desktop with a Python runtime for tool use. Devices share one account and sync conversations through a relay (self-hostable), while the agent proactively acts, retains memory, and pauses before irreversible actions; it is released GPL-3.0-or-later with documentation on install, self-hosting, connectors, and memory.
github.comrepoPublished and added 7 Oct 2026🧠 AI  The Vulnerable MCP Project — MCP vulnerability database
The Vulnerable MCP Project is a curated, continuously growing database of security vulnerabilities and attack techniques specific to the Model Context Protocol ecosystem. Entries cover concrete CVEs (e.g. CVE-2025-68143/68144/68145 in Anthropic's mcp-server-git), transport-layer SDK flaws (cross-client response leakage, missing DNS rebinding protection in the official TypeScript/Python SDKs), unauthenticated/0.0.0.0-bound servers enabling RCE (MCPJam inspector, MCP Inspector, Grafana MCP), command/path injection in dozens of third-party servers (gemini-mcp-tool, mcp-server-kubernetes, Framelink Figma MCP, Zen MCP, filesystem-mcp), SSRF chains reaching cloud metadata (MarkItDown MCP, mcp-fetch-server), and a large set of AI-specific attacks: tool poisoning, trigger-phrase data exfiltration, prompt injection via GitHub issues, Jira and Google Docs, rug-pull tool mutation, and cross-server tool-name collisions. It functions as the de facto vulnerability registry for the MCP ecosystem, useful for tracking disclosed issues before patching or adopting third-party MCP servers.
 vulnerablemcp.inforepoAdded 6 Oct 2026🛡️ Security
- Microsoft Agent Framework python-1.20.0 release
Release notes for python-1.20.0 of Microsoft's Agent Framework, an open-source agent/workflow orchestration library. This release adds native vector-store connectors for DuckDB, SQL Server and MongoDB plus a TypeSafe AI connector, redesigns Foundry hosting around request-scoped agent factories and sandbox-isolated sessions, adds computer-use support to Responses clients, and ships Magentic manager and handoff-routing improvements for multi-agent orchestrations alongside a large batch of MCP, Bedrock, Gemini, Anthropic and Ollama provider fixes.
github.comrepoAdded 6 Oct 2026🧠 AI - Show HN: OpenChart – OSS TradingView alternative with your own AI agent
OpenChart is an open-source TradingView-style desktop charting app (Electron, Node.js/Bun, Effect runtime) that embeds AI agents into statistical/technical analysis, real-time market alerts and agentic opportunity research. It ships a custom DSL called Tea (inspired by TradingView's Pine Script) for writing indicators, and a conversation interface built on assistant-ui and the AG-UI event protocol so users converse with agents while charting.
github.comrepoPublished and added 6 Oct 2026🧠 AI - browser-use/jev-ultrafast
jev-ultrafast is an open-source browser automation agent (from Browser Use) that represents each page as an indexed element table and uses a 'TypeSafe' policy to speculatively predict both the next operation (CLICK, TYPE_TEXT, SELECT, SCROLL, WAIT, DONE, BLOCKED) and its target in a single network round trip, only invoking a small LLM (e.g. inception/mercury-2.5 via OpenRouter) to generate text when the operation is TYPE_TEXT. The repo includes a local inspector UI, Chrome automation via a 'Browser Harness' tool, offline tests, and published before/after benchmarks showing a Google Flights search dropping from a median 9.45s to 7.09s and browser protocol calls from 1,092 to 101 across repeated runs.
github.comrepoAdded 6 Oct 2026🧠 AI - overmind-core/overmind
Overmind is an open-source platform (MIT SDK/CLI, AGPL-3.0 platform, self-hostable) that instruments an agent's code via OpenTelemetry tracing, turns the resulting production traces (or any dataset) into a fine-tuned model benchmarked against user-defined eval metrics, and serves it through one unified API with downloadable/retrainable weights. It ships an SDK, CLI, REST API, Console, and an MCP server exposing project tools and workflows (investigate-capability, finetune-capability, ship-model) for Cursor, Claude Code, OpenCode and Codex, and can sync traces from Langfuse, LangSmith, Braintrust or Galileo; self-hosting runs via Docker Compose with Postgres, Redis, Celery workers and Modal-based GPU workers for fine-tuning/serving (vLLM).
github.comrepoAdded 6 Oct 2026🧠 AI - claude-mem — persistent memory system for Claude Code and other coding agents
Claude-Mem is an open-source persistent memory plugin for Claude Code and other coding agents (Codex, OpenCode, Grok Bot, T3 Code, OpenClaw) that captures tool-usage observations during sessions, compresses them into semantic summaries, and reinjects relevant context into future sessions. It uses five lifecycle hooks (SessionStart, UserPromptSubmit, PostToolUse, Stop, SessionEnd), a local SQLite database, a Chroma vector store for hybrid semantic+keyword search, and exposes three MCP tools (search, timeline, get_observations) that follow a token-efficient layered retrieval pattern to cut context costs roughly 10x. It is Apache-2.0 licensed, built with the Claude Agent SDK and TypeScript, and ships an optional hosted "observer" memory service alongside self-hosted options via OpenRouter/Gemini keys or an Anthropic plan.
github.comrepoAdded 5 Oct 2026🧠 AI - Dark Web Informer (@DarkWebInformer) on X
A public PoC chains CVE-2026-42589 and CVE-2026-40281 to achieve unauthenticated remote code execution against Gotenberg (a document/PDF-conversion microservice), abusing metadata injection flaws in the /forms/pdfengines/metadata/write endpoint. The tool supports vulnerability detection, interactive command execution, reverse shell delivery, and multi-target scanning against Gotenberg versions ≤8.30.1 (patched in 8.31.0).
x.comrepoPublished and added 5 Oct 2026🛡️ Security - Zhenyu98/codex-chatgpt-bridge
codex-chatgpt-bridge is a Codex agent skill plus external PowerShell control scripts (On/Off/Reboot/Rotate) built on top of the open-source DevSpace MCP bridge, which lets ChatGPT act as a planning/review "architect" while Codex stays the local executor that applies and verifies changes. It adds a token-saving router (NORMAL / TOKEN_SAVING / CHATGPT_ARCHITECT modes) and a lifecycle layer — Cloudflare Quick Tunnels or a stable Cloudflare Worker proxy, DPAPI-protected credentials, OAuth token rotation, and a scheduled-task recovery entrypoint — so the bridge's public endpoint can be closed when idle without re-authorizing the ChatGPT app on every restart.
github.comrepoAdded 5 Oct 2026🧠 AI - the_OSINT_rack (@the_OSINT_rack) on X
Vinted_OSINT is a GitHub tool by EchterAlsFake that performs open-source intelligence gathering against Vinted.com user profiles, pulling seller/buyer account information and computing a risk score to flag accounts likely run by scammers. It's aimed at buyers wanting to vet sellers before transacting on the second-hand marketplace.
x.comrepoPublished and added 4 Oct 2026🛡️ Security - M-med/Active-Directory-Simulation-Attack-
Active-Directory-Simulation-Attack- is a purple team lab for the lab.local domain (192.168.100.0/24). It walks through an attack chain: BloodHound/SharpHound recon, Kerberoasting, hash cracking with John the Ripper or Hashcat, and lateral movement with Impacket. It then applies hardening (gMSA, tiering, LLMNR/NetBIOS disabling) and adds Sysmon, Wazuh SIEM and custom Kerberoasting rules (Event ID 4769, RC4).
github.comrepoAdded 23 Oct 2026, published 4 Oct 2026🛡️ Security - DeepZero
DeepZero is an open-source orchestration engine that lets researchers define vulnerability-research pipelines declaratively in YAML, handling parallel execution (ThreadPoolExecutor), resumable/fault-tolerant state, and LLM-assessment stages via LiteLLM/Jinja2 prompts. It ships example processors for Ghidra headless decompilation, LOLDrivers.io hash exclusion filtering, PE header/driver metadata extraction, and batch Semgrep scanning, with a dedicated pipeline for BYOVD kernel driver vulnerability research. An extensibility model lets users plug in custom Python processors referenced by path in the YAML config.
github.comrepoAdded 3 Oct 2026🛡️ Security - Sigma r2026-07-01 — 20 new detection rules
GitHub release notes for Sigma r2026-07-01, the open-source detection-rule repository, adding 20 new rules (e.g. LSASS crash via Netlogon buffer overflow CVE-2026-41089, TanStack supply-chain attack indicators for Windows/Linux, RedTail cryptominer user-agent detection, AF_ALG kernel crypto API exploit indicator) and updating/fixing dozens of existing rules for ARM64 binary variants, file-sharing domain IOCs, and WMI-based reconnaissance/persistence detection. It's a routine but substantive update to a widely-used blue-team detection content pack.
github.comrepoAdded 3 Oct 2026🛡️ Security - jiwoochris/artex-global
ARTEX global edition is an English-default fork of the Chinese open-source ARTEX (AGPL-3.0), an autonomous penetration-testing system in which planner and worker LLM agents run real tools and record results in an asset graph and an exploration graph on PostgreSQL. It also ships a defense guide, Sigma and Suricata rules, an ATT&CK Navigator layer, MISP indicators and a host triage script for spotting ARTEX-driven attacks.
github.comrepoAdded 31 Oct 2026, published 3 Oct 2026🛡️ Security - Jakeschincariol/replica-skill
replica-skill is an MIT-licensed set of eleven Claude skills that run an app-cloning pipeline: recon, architect, design, build, backend, test, diff, entrepreneur, brand, launch and deploy. Six standard-library Python tools handle image diffing, parity scoring, review ranking, contrast checks, rebrand sweeps and store-listing lint. It installs as a Claude Code plugin or by copying folders, and states clean-room and rebranding limits.
github.comrepoAdded 29 Oct 2026, published 3 Oct 2026🧠 AI - OKX Agent Trade Kit (okx-trade-mcp / okx-trade-cli)
OKX Agent Trade Kit is an open-source MCP server (okx-trade-mcp) and CLI (okx-trade-cli) that let AI assistants like Claude Desktop, Cursor, Claude Code and VS Code place trades and query account data on the OKX exchange via natural-language commands. It runs locally with API keys never leaving the machine, supports module scoping (market, spot, swap, account, earn), a read-only mode for safe querying, multiple profiles, and includes pre-built skill files for agent frameworks plus structured JSON error reporting for debugging failed tool calls.
github.comrepoAdded 2 Oct 2026🧠 AI - Show HN: Made an open-source Lego AI generator
ldraw-nova is an open-source agentic pipeline where an LLM agent (tested with models like Claude Opus 5.5 and GPT-6 Astra) takes a build prompt, reads LDraw-building instructions, and produces a plan.json describing a model's geometry. From that plan it writes a Python generator script that, when executed, outputs an LDraw (.mpd) 3D CAD source file, viewable in 3D/VR (Meta Quest 3) or exportable to Blender-editable glTF. The agent uses jev-rerank, a semantic search tool with reranking backed by TypeSafe's Jev System One model, to find suitable LEGO parts and example models, falling back to full-text search without an API key; it also uses headless rendering and collision/gap detection to self-inspect and iterate on designs.
github.comrepoAdded 3 Oct 2026, published 2 Oct 2026🧠 AI - Microsoft Agent Framework — python-1.20.0 release
Release notes for Microsoft's Agent Framework (Python and .NET SDKs), covering versions python-1.16 through python-1.20 and dotnet-1.19 through dotnet-1.23. Changes span native vector-store connectors (MongoDB, Qdrant, PostgreSQL/pgvector, DuckDB, SQL Server, Azure Cosmos DB, Azure AI Search), Foundry hosting redesigns around request-scoped agent factories and durable Invocations, MCP skill/session security hardening (approval binding, security labels, ZIP-only skill archives), Magentic multi-agent orchestration and handoff routing, and checkpoint/replay correctness fixes across workflows.
github.comrepoAdded 2 Oct 2026🧠 AI  Kyutai Pocket TTS
Pocket TTS is a 100M-parameter text-to-speech model from Kyutai designed to run efficiently on CPU, generating audio faster than real-time (~6x on a MacBook Air M4) with ~200ms latency to first audio chunk and voice cloning from short audio samples. It supports English, French, German, Portuguese, Italian, and Spanish, ships a Python library and CLI, and has spawned numerous community ports (WASM, ONNX, Rust/Candle, MLX, C++, C#) and fine-tuned language variants (Czech, Hindi, Korean, Persian, Indonesian, Estonian, Welsh, Polish).
huggingface.corepoAdded 2 Oct 2026🧠 AI Tencent Hy4 preview (open-weight MoE + Sherry quantization)
Hy4 preview is Tencent's new flagship Mixture-of-Experts language model: 770B total parameters with 49B activated per token across 78 layers (256 routed experts + 1 shared expert, top-8 routing), plus a native 10B multi-token-prediction layer for speculative decoding. It introduces Gated DeepSeek Sparse Attention with IndexCache for cross-layer index reuse and identity Hyper-Connections (iHC) on the residual path, and in blind internal evaluations on engineering tasks it edges out GLM-5.3 and Kimi K3. Weights (including an FP8 variant) are released under Apache 2.0 on Hugging Face with vLLM/SGLang deployment recipes and AngelSlim-based quantization/compression tooling.
huggingface.corepoAdded 2 Oct 2026🧠 AI- Bifrost (Maxim AI) — open-source LLM gateway
Bifrost is an open-source, high-performance LLM gateway (by Maxim AI) that exposes a single OpenAI-compatible API across 23+ providers including OpenAI, Anthropic, AWS Bedrock, Google Vertex, Azure, Cohere, Mistral, and Ollama. It provides automatic failover, load balancing, semantic caching, Model Context Protocol (MCP) tool integration, budget and governance controls, OIDC user provisioning, and Prometheus-based observability, deployable via npx or Docker with claimed sub-15 microsecond overhead at 5,000 RPS. It is positioned as a drop-in replacement requiring only a base-URL change for existing OpenAI, Anthropic, or GenAI SDK code.
github.comrepoAdded 2 Oct 2026🧠 AI - NuvexNetwork/nuvex
Nuvex is a Solana-native verifiable compute and oracle protocol, still pre-mainnet, whose own README documents unresolved security gaps instead of hiding them: its VRF proof verification relies on solana-ecvrf 0.0.1 (RFC 9381 ECVRF-Edwards25519-SHA512-TAI) which has no known audit, max_fee is stored but never actually charged, and VRF fulfillment is first-come among any node meeting the configured stake/heartbeat threshold — meaning an operator who funds several keys at a low minimum stake can selectively pick which randomness output gets used. The deploy-mainnet script is stubbed to exit before any transaction, and unresolved design questions (fee shares, challenge/reject state transitions) are tracked as explicitly blocked ADRs rather than quietly shipped.
github.comrepoPublished and added 2 Oct 2026🛡️ Security - Folkbench/folkbench
Folkbench has two parts. One is a public benchmark and leaderboard of third-party AI API relay (中转站) services. Multi-node probes run around the clock and publish availability, P95 latency and price per relay, with per-model rankings. The other is Switch, an open-source Tauri/Rust desktop client that stores several Base URL and API Key pairs. It applies them to Claude Code or Codex configs in one click, previews config diffs, and stashes and restores the official ChatGPT OAuth credentials when switching Codex to a third-party provider. It also keeps keys local and estimates token usage and cost per session. The README also profiles several relay services, such as Modelflare, CheapAI and ApiPorter, and that part reads as promotional.
github.comrepoAdded 12 Oct 2026, published 2 Oct 2026🧠 AI - renato-osec/goonfi-v2-decompiled
goonfi-v2-decompiled holds byte-identical reconstructed Rust source for the GoonFi V2 Solana program goonuddtQRrWqqn5nFyczVKaie28f3kDkHWkHtURSLE, as deployed at slot 448984043. The on-chain program was upgraded on 6 October 2026 to fix reported bugs. VERIFY.sh builds with Solana platform-tools v1.48 and compares the result to the deploy transaction's loader buffer writes. The page does not describe the bugs.
github.comrepoAdded 22 Oct 2026, published 2 Oct 2026🛡️ Security - zzzz7788990213-ops/EvoVLM
EvoVLM searches over prompts, image preprocessing, generation budgets and answer extraction for frozen Qwen3-VL-2B-Instruct and Qwen3-VL-2B-Thinking, without fine-tuning weights. A local Qwen model ranks a catalog of typed mutations, a trusted renderer produces Python programs, and Pareto selection on accuracy and latency drives two small generations on scientific chart understanding (CharXiv subset). Recorded results on Dev128: Evolved Instruct keeps accuracy with 8.9% lower median latency, and Evolved Thinking gains 16.41 points of accuracy with 10.6% lower median latency. CPU-only replay and fail-closed evidence verification are included. The authors state the limits: small sample, overlap with the evolution set, and results tied to the recorded hardware.
github.comrepoAdded 16 Oct 2026, published 2 Oct 2026🧠 AI - NVIDIA/OpenShell — sandboxed runtime for autonomous AI agents
OpenShell is NVIDIA's open-source runtime for safely running fleets of autonomous AI agents: each agent runs in an isolated sandbox where kernel-level controls enforce a declared policy over file access, syscalls, and network connections, and credentials are injected only for approved endpoints rather than exposed to the agent directly. Policy changes are checked with formal verification to flag risky new access (new hosts, new API methods) before they're approved, and the project ships a CLI, gateway, Kubernetes/Helm deployment, and a tutorial running OpenCode against an OpenRouter model.
github.comrepoAdded 1 Oct 2026🛡️ Security - MITRE ATLAS v2026.08 release — autonomous agent techniques
Release notes for MITRE ATLAS v2026.08, the adversarial AI/ML knowledge base (now 1 matrix, 16 tactics, 114 techniques, 83 sub-techniques, 39 mitigations, 72 case studies). This version renames the "AI Attack Staging" tactic to "AI Attack Adaptation," generalizes several techniques (e.g., Cloud Service Discovery → Enterprise Resource Discovery, Process Discovery → Enterprise Environment Discovery, Reverse Shell → Cyber Communication Channel), and updates mitigations and techniques like LLM Prompt Crafting and Retrieval Content Crafting.
github.comrepoAdded 1 Oct 2026🛡️ Security - OpenShell — safe, private runtime for autonomous AI agent fleets
OpenShell is NVIDIA's open-source runtime for running fleets of autonomous AI agents inside isolated sandboxes. Declarative policies cover filesystem, syscall, process and network access. These are enforced at the kernel level, and credentials are injected only into requests bound for approved endpoints. Policy changes are checked with formal verification so risky new access waits for human review. It ships a CLI, a gateway control plane (Helm deployment on Kubernetes), SDKs, extensibility hooks (middleware, interceptors, compute drivers) and installable agent skills, and it can run agents such as OpenCode.
github.comrepoAdded 1 Oct 2026🧠 AI - ShadowSafin/Synapass
Synapass is an OpenAI-compatible inference gateway and control plane that decides per request which AI provider serves it, under policy. It provides routing, retry and failover, exact/prefix/semantic caching, rate limits and budgets, tenant isolation, and an explain endpoint recording why each request was routed. It deploys with one command via Docker Compose (Postgres, Redis, ClickHouse, NATS, Grafana stack, dashboard).
github.comrepoAdded 20 Oct 2026, published 1 Oct 2026🧠 AI - https://github.com/Panniantong/Agent-Reach
Agent-Reach is a CLI and agent-"skill" layer that equips coding agents (Claude Code, Cursor, OpenClaw) with ready-made web-reading tool use: fetching arbitrary pages via Jina Reader, YouTube transcripts via yt-dlp, GitHub repos via gh CLI, Bilibili search, RSS via feedparser, and semantic web search via Exa through mcporter, with login-gated platforms (Twitter/X, Reddit, Xiaohongshu, Facebook, Instagram) added on request via cookies or OpenCLI browser sessions. Each platform module probes an ordered list of candidate backends and falls back automatically when one breaks (e.g. yt-dlp being blocked by Bilibili's anti-scraping), and an `agent-reach doctor` command reports which backend each channel is currently using. It positions itself as a "capability layer" that selects, installs and health-checks the right upstream tool for an agent rather than wrapping the reads itself.
github.comrepoAdded 2 Oct 2026, published 1 Oct 2026🧠 AI - AI-Infra-Guard (A.I.G) — Tencent Zhuque Lab
AI-Infra-Guard (A.I.G) is Tencent Zhuque Lab's open-source AI red-teaming platform combining AI infrastructure vulnerability scanning (2000+ CVE rules covering vLLM, llama.cpp, LangFlow, n8n, MLflow and 145+ other AI components), MCP server/skill security scanning, LLM API poisoning detection, and multi-turn jailbreak evaluation (Many-Shot, PAIR, GOAT, ActorAttack). It ships CLI tools (skill-scan, mcp-scan, agent-scan), a Docker-deployed web UI, and has produced original research including FORGE-Bench (loss-of-control benchmark), RogueHandoff-20, and SkillJack (persistent skill backdoors), with talks at Black Hat Europe 2025 on MCP security.
github.comrepoAdded 30 Sep 2026🛡️ Security - Sift — Open-Source Secrets/Credential Scanner
Sift is Stratus Security's open-source successor to Snaffler: a Native AOT credential/secrets scanner for pentesters that crawls local drives, SMB shares/subnets, Active Directory, SharePoint/OneDrive/Teams, Slack, and Jira/Confluence for exposed secrets. It supports Kerberos/NTLM/pass-the-hash authentication, resumable checkpointed scans, a JSON rule/ignore-rule system compatible with Snaffler's detection catalogue, and optional local-LLM (Ollama) validation to cut false positives without sending sensitive findings to a cloud API.
github.comrepoAdded 30 Sep 2026🛡️ Security - CAIRN — Cisco Talos AI-Malware-Hunting Toolkit
CAIRN is a Cisco Talos research toolkit that identifies and attributes AI-integrated malware purely from VirusTotal metadata — no binary downloads or detonation — by running a tiered YARA ontology (T1/T2/T3) over composed scan text (AV strings, PE resources, Sigma/sandbox behavioral data, embedded URLs) and layering on sentence-transformer embeddings with HDBSCAN clustering for semantic family attribution. It has produced confirmed family reports for AI-malware such as PROMPTLOCK, LAMEHUG, PROMPTSTEAL, QUIETVAULT, CLOSEDQUORUM, and FRUITSHELL, each cross-verified by hands-on Talos reverse engineering before publication.
github.comrepoAdded 30 Sep 2026🛡️ Security  DeepSeek-V4.1-Flash
 is a multimodal Mixture-of-Experts model with 552B backbone parameters, 1M-token context, and a novel Causal Encoder-Decoder (CED) architecture where the decoder's global KV cache is projected from encoder hidden states rather than recomputed per layer, activating only 8B/16B parameters per token during prefill/decode. It introduces Compressed Sparse Attention 2 (CSA2) with FP4 KV caching to cut the global KV cache footprint to 890 bytes/token (~1/4 of DeepSeek-V4-Flash, ~1/437 of DeepSeek-V1), alongside Engram conditional memory, DSpark speculative decoding, and a continuously controllable reasoning-effort setting (1–100). The card documents pre/post-training recipes (45T tokens, SFT→RL→on-policy distillation with synthetic agent environments) and reports results across agentic and code benchmarks (Terminal-Bench 2.1/3.0/4.0, DeepSWE v1.1, GPQA Diamond, Chartography, ZeroBench, AutomationBench), plus deployment instructions for Transformers, vLLM, SGLang, and Docker.
huggingface.corepoAdded 30 Sep 2026🧠 AI- Launch HN: Magnitude (YC S25) – Self-optimizing inference engine for agents
Magnitude is an open source local inference engine (Apache 2.0) that compiles and tunes its GPU/CPU kernels on the user's exact device before a model runs, claiming up to 2x faster decode than llama.cpp (92% faster on Metal, 19% on CUDA) with 27% lower memory per agent. It ships as a cross-platform desktop app with a bundled CLI and an OpenAI-compatible API, offering one-click connections to agent tools like Pi, OpenCode, Hermes, Codex, OpenClaw, Claude Code, and Cline, running fully offline on Apple Silicon, NVIDIA, AMD, or CPU-only hardware.
github.comrepoPublished and added 30 Sep 2026🧠 AI - Andrea (Drego) Draghetti 👨🏻💻 🎣 (@AndreaDraghetti) on X
Tosint v1.0.0 is an open-source Telegram OSINT tool for analyzing bots and chats, exporting message history and media. The new release adds richer JSONL metadata output, optional SHA-256 hashing of exported media, bot/user authentication support, and an automatic fallback from MTProto-based history retrieval to ID-scan mode when dealing with restricted chats.
x.comrepoAdded 2 Oct 2026, published 30 Sep 2026🛡️ Security - AI News | AI Tools (@AI_News100x) on X
Open-Dots is an open-source reimplementation of OpenAI's 'Dots' computer-use agent, giving any LLM the ability to control a browser, terminal and filesystem plus connectors to personal apps. It is framework-agnostic (works with any LLM) and free, positioned as a self-hostable alternative to OpenAI's proprietary computer-use offering.
x.comrepoPublished and added 30 Sep 2026🧠 AI - rehan-remade/universal-modder
universal-modder is a set of Agent Skills, a CLI (um) and a shared knowledge base (field notes in knowledge/) that let AI coding agents such as Claude Code, Codex, Gemini CLI, Cursor, GitHub Copilot and OpenCode find a PC game's engine, reverse-engineer its code, build a working mod, generate art/3D/sound assets via the fal MCP server (or a local ComfyUI server), test the mod in the running game, and write a field note for the next agent. It ships worked examples — a weapon/boss pack for Terraria via tModLoader, a new civilization for Age of Empires II DE, and a real-time Minecraft-inside-GTA-V passthrough mod — each documented with a field note of exact versions, routes and gotchas, and agents can open pull requests to grow the shared knowledge base.
github.comrepoAdded 6 Oct 2026, published 30 Sep 2026🧠 AI  רון אברבוך (@Ron_averbuch) on X
Open-Dots is an open-source re-implementation of OpenAI's Dots computer-use agent, giving it browser, terminal and file control plus connectors to personal apps, and designed to work with any LLM rather than being locked to one vendor's model. It's announced via a tweet linking to the GitHub repo (github.com/Anil-matcha/Open-Dots).
x.comrepoAdded 30 Sep 2026, published 29 Sep 2026🧠 AI- feder-cr/invisible_playwright_mcp
invisible_playwright_mcp is an MCP server (and companion Python library, invisible_playwright) that wraps Playwright so an LLM agent can operate a real browser like a human: clicking, typing, scrolling and reading page content, useful for tasks like checking flight fares across a date range where no API exists. It ships a standalone chat+live-browser UI driven by any OpenRouter model, installs as a plugin for Claude Code, Codex and Gemini CLI, and exposes stealth/identity controls (seed-based browser fingerprint, proxy-derived timezone/locale/geolocation, persistent profile directories) via its invisible_core component.
github.comrepoAdded 7 Oct 2026, published 29 Sep 2026🧠 AI - NVIDIA OpenShell — secure runtime for autonomous AI agent fleets
OpenShell is NVIDIA's open-source runtime for running fleets of autonomous AI agents with restricted, policy-governed access to files, system calls, network, and credentials. It enforces policy at the kernel level inside isolated sandboxes (per-agent, with Docker/Podman/virtualization backends) and uses formal verification to flag risky policy changes — such as an agent gaining a new host or API access with credentials — before they take effect, so changes can wait for human review. It ships a CLI, a gateway control plane, Kubernetes/Helm deployment, and installable agent skills for writing and debugging sandbox policies.
github.comrepoAdded 29 Sep 2026🧠 AI - garak v0.17.0 — LLM vulnerability scanner release
Release notes for garak v0.17.0, NVIDIA's open-source LLM vulnerability scanner used for red-teaming and probing models for jailbreaks, prompt injection, data leakage and other failure modes. The release adds an EU AI Act risk-category mapping to tag and group probe results, plus fixes to detectors (agent_breaker judge verdict validation, packagehallucination import parsing, MarkdownExfilContent divide-by-zero, TriggerListDetector alignment) and probes (badchars ASCII selection, Markdown exfiltration link templates), along with Ollama generator improvements and dropped Python 3.10 support in favor of 3.13.
github.comrepoAdded 29 Sep 2026🛡️ Security - NVIDIA OpenShell — secure runtime for autonomous AI agent fleets
OpenShell is NVIDIA's open-source runtime for running fleets of autonomous AI agents in isolated sandboxes, enforcing per-agent policies on filesystem, syscall, and network access at the kernel level and injecting credentials only for approved endpoints. Policy changes go through a formal-verification step (an 'advisor'/'prover') that flags newly granted risky access, such as a new host reachable with credentials, before it's applied, and it deploys via Docker/Podman/host virtualization or Kubernetes with Helm.
github.comrepoAdded 29 Sep 2026🛡️ Security  Ternary-Bonsai-2-27B: 27B model compressed to ~1.75 bits/weight, 98.2% of FP16 quality retained
Ternary-Bonsai-2-27B is a 27B-parameter reasoning model (built on Qwen3.8-27B) quantized to true ternary weights ({-1,0,+1}) at ~1.72 bits/weight, shrinking it from ~54GB FP16 to ~5.95GB while retaining 98.2% of FP16 benchmark quality (84.78 vs the conventional sub-4-bit IQ2_XXS build's 72.59). It uses a Hadamard-rotated weight basis and ships two GGUF packing formats (PTQ1_0 dense trits, PQ2_0 2-bit slots) that require a custom llama.cpp/MLX kernel fork since stock llama.cpp cannot decode them correctly. The card includes per-category benchmark breakdowns (math, coding, agentic tool calling), cross-platform throughput/power measurements (Apple M5 Pro/Max, RTX 5090, L4, H100/A100/Blackwell), and an "intelligence density" metric comparing capability retained per GB against FP16 and other quantizations.
huggingface.corepoAdded 29 Sep 2026🧠 AI MiMo-V2.6 (Xiaomi): Pro/Flash/9B-distill open-weight release, MIT license, 1M context
Hugging Face collection for Xiaomi's MiMo-V2.6 model family, comprising five open-weight checkpoints: MiMo-V2.6-Pro-RL (1T params), MiMo-V2.6-Flash-RL (311B params), a MiMo-V2.6-Distill-Qwen-9B distillation (vision-language capable), and Pro/Flash MOPD variants. The title claims MIT licensing and a 1M-token context window, positioning this as a large open-weight release spanning full-scale RL-trained models down to a 9B distilled variant usable on consumer hardware.
huggingface.corepoAdded 29 Sep 2026🧠 AI- https://github.com/dmdhrumilmistry/security-harness
security-harness is an open-source Claude Code plugin (also packaged for Gemini CLI, Codex and opencode) that orchestrates subagents — sh-recon, sh-hunter, sh-chainer, sh-verifier, sh-reporter — through a static-analysis pipeline covering 15 vulnerability classes (IDOR/BOLA, SQLi, XSS, SSRF, injection, auth, deserialization, path traversal, secrets, CSRF, XXE, open redirect, crypto, race conditions, file upload), producing README/JSON/SARIF/HTML/PDF reports with PoCs, CVSS and CWE/OWASP mappings. It also ships sh-pr-review, a per-PR merge-gate skill that posts inline findings and a commit status scoped only to code the PR itself introduced or aggravated, with caching, dedup via fingerprints, and a scheduled GitHub Action that keeps its per-class knowledge bases fresh by having one AI agent draft updates from allowlisted sources (OWASP, PortSwigger Research, CWE/CAPEC, HackerOne) while a separate adversarial reviewer agent fails-closed against prompt injection before auto-merge.
github.comrepoAdded 2 Oct 2026, published 29 Sep 2026🛡️ Security - StartLuxLabs/StartLux-Decision
StartLux-Decision is a family of open decision models (0.8B to 27B, plus a 35B-A3B mixture of experts) that return probabilities for every option of typed choice, yes/no and score questions. The repository holds the inference engine and HTTP server (vLLM plugin, /v1/systemone API), with Instant one-pass and AutoThink gated-reasoning variants. Reports first place of 174 entries on Decision Index 0.3.2 (69.12). Code is Apache 2.0; weights are CC BY-NC 4.0.
github.comrepoAdded 23 Oct 2026, published 29 Sep 2026🧠 AI - Uncensored and Offensive Security AI Models Benchmark
A curated GitHub list of open-weight "uncensored" and security-fine-tuned LLMs intended for authorized red teaming, pentesting, and security research, covering models like WhiteRabbitNeo's DeepHat V2, BugTraceAI-CORE, CYBER-FROST, and several abliterated Qwen/GLM/DeepSeek variants. It explains the underlying techniques (abliteration per Arditi et al. 2024, QLoRA/DPO fine-tuning, GGUF/FP8 quantization) and links to Hugging Face model cards, benchmark suites (CyberBench, TrustedSec's LLM Attack Benchmark vs OWASP Juice Shop), and deployment platforms for running these models locally or via API.
github.comrepoAdded 2 Oct 2026, published 29 Sep 2026🛡️ Security - Uncensored and Offensive Security AI Models Benchmark
A GitHub README curating open-weight "uncensored" and security-fine-tuned LLMs (e.g. WhiteRabbitNeo's DeepHat V2, BugTraceAI-CORE, CYBER-FROST, CyberPal2.0, Lily-Cybersecurity-7B, Dolphin-Llama3-8B, Wizard-Vicuna-13B-Uncensored, huihui-ai's abliterated Qwen variants) with HuggingFace download links, quantization formats (GGUF, FP8, Q4_K_M, Q6_K), and training techniques used (SFT, QLoRA, DPO, abliteration, MoE/MTP architectures). It also includes a glossary explaining abliteration (orthogonalizing the refusal direction out of the residual stream, per Arditi et al. 2024) and references benchmarks like CyberBench and TrustedSec's LLM Attack Benchmark, making it a practical reference for anyone sourcing or deploying refusal-removed models.
github.comrepoAdded 2 Oct 2026, published 29 Sep 2026🧠 AI - openrig — multi-agent Claude Code/Codex orchestration
OpenRig is an open-source local daemon/CLI/TUI/MCP server that orchestrates teams of Claude Code and Codex agent sessions (via tmux) defined declaratively in YAML "RigSpecs." Its own docs disclose a significant trust/permission footprint: it writes workspace-trust settings and status-line/activity hooks into ~/.claude.json and .claude/settings.local.json, pre-writes Codex trust hashes and trusted workspace entries into ~/.codex/config.toml, defaults Claude to --permission-mode acceptEdits and Codex to -s workspace-write, and supports an explicit OPENRIG_YOLO=1 mode that enables Claude's --dangerously-skip-permissions or Codex's -s danger-full-access. It also relays session/activity telemetry to a local daemon endpoint.
github.comrepoAdded 28 Sep 2026🛡️ Security - openrig — multi-agent Claude Code/Codex orchestration
OpenRig is an open-source local daemon, CLI, TUI and MCP server (built on tmux + SQLite) that manages teams of Claude Code and Codex agent sessions as a single persistent system rather than a pile of terminal windows. Topologies (pods, seats, edges) are defined declaratively in YAML (RigSpec/AgentSpec), booted with `rig up`, inspected via a topology TUI, and can be snapshotted/restored, discovered from existing tmux sessions, and messaged across agents (`rig send`, `rig broadcast`, `rig chatroom`). It ships starter topologies (first-project, conveyor, product-team, secrets-manager using HashiCorp Vault) and documents in detail what it writes to Claude/Codex config, trust and telemetry state on the host machine.
github.comrepoAdded 28 Sep 2026🧠 AI - vLLM v0.30.0
Release notes for vLLM v0.30.0, a major update to the open-source LLM inference/serving engine spanning 762 commits. Highlights include new model support (DeepSeek-V4.1-Flash, GLM-5.3-Flash, Kimi K3, Qwen3.8-Flash-Next, K2-Horizon, Cohere Compass and others), a "Fast Start" GPU weight-cache daemon for near-instant engine restarts via CUDA IPC, Gumbel-max watermarking for generated text, a HiSparse host-memory tier for sparse-MLA KV offload, Model Runner V2 improvements (dual-batch overlap, speculative decoding under pipeline parallelism), expanded quantization support (NVFP4, W4A16 DSA, AutoRound), and hardware-specific tuning across NVIDIA, AMD ROCm, Intel XPU and CPU backends.
github.comrepoAdded 28 Sep 2026🧠 AI  MiMo-V2.6-Pro-RL
 is Xiaomi's flagship omnimodal (text/image/video/audio) sparse MoE model, 1.02T total / 42B activated parameters with a 1M-token context, built around scaling RL compute toward self-improvement. It uses a single mixed GRPO run across coding, agentic, visual and cybersecurity tasks, a novel groupwise agentic grading scheme (Groupwise Reward Synthesis + Groupwise Advantage Redistribution) to rank passing rollouts rather than just pass/fail, and a multi-teacher on-policy distillation stage (MOPD2); it also ships a 5-layer speculative MTP decoder and is deployable via vLLM and SGLang.
huggingface.corepoAdded 28 Sep 2026🧠 AI- dagoSte/squadra
Squadra (version 3.11.0) is an MIT-licensed Python 3.12+ tool that coordinates several Claude Code, Codex and interactive Cursor windows on one project through a shared local registry. It records tasks, acknowledgements, source-bound proofs and independent reviews by a window that did not write the code. A local dashboard shows progress, per-window token usage and model-balance suggestions, and community plugins extend it. The page was truncated, so later sections are not covered.
github.comrepoAdded 27 Oct 2026, published 28 Sep 2026🧠 AI - SpecterOps/Blacklight — local AI agent attack surface mapping toolkit
Blacklight is a SpecterOps toolkit for endpoint forensics on AI coding agents, split into Scout (bounded metadata/filesystem triage across Codex, Claude Code, Cursor, Antigravity CLI, and Grok that finds candidate session artifacts without reading their contents) and Session Analysis (a Python CLI that parses selected JSONL/SQLite session downloads from Codex, Claude Code, Cursor, and Antigravity CLI into ranked, redacted local reports). It's built for investigators who need to identify and review AI agent session history on a host — surfacing config, auth metadata, and high-value indicators — while explicitly leaving secret scanning to external tooling; paths are informed by SpecterOps' Endpoint AI Agent Abuse (EAA) technique catalog.
github.comrepoAdded 27 Sep 2026🛡️ Security - Paper2Agent: research papers as interactive AI agents
Paper2Agent is a multi-agent AI system that coordinates parallel specialist agents to transform a research paper and its code repository into a tested MCP server exposing the paper's methods as callable tools ('agentified' papers). It ships as a skill for coding agents like Claude Code and Codex, and the project demonstrates the pipeline on real papers (TISSUE for spatial transcriptomics, Scanpy for single-cell analysis, AlphaGenome for genomic variant interpretation), each producing a hosted MCP server that a chat agent can call to run the paper's actual scientific workflows.
github.comrepoAdded 27 Sep 2026🧠 AI - Adversarial-Detection-Engineering/adeskills
adeskills is a working knowledge base for "Adversarial Detection Engineering" (ADE), a taxonomy of four categories and 16 subcategories of detection-logic bugs (e.g. Reformatting in Actions, Omit Alternatives, Context Development, Logic Manipulation) that explain why a SIEM/EDR/XDR rule fails to catch what it intends to. It ships 38 worked technique files with vulnerable/hardened rule examples and detection-layer guidance, a cross-platform bug-pattern catalog, a pre-engagement scoping checklist, and a Redamon-packaged skill (ade_scoper), all grounded in analysis of real public rulesets from Sigma, Elastic Security, and Microsoft Sentinel. It's explicitly scoped for defensive detection engineering and purple-team rule hardening, with several files documenting real vendor-rule weaknesses.
github.comrepoAdded 2 Oct 2026, published 27 Sep 2026🛡️ Security - zhuyansen/awesome-claude-video-skills
Awesome-list repository cataloguing 183 open-source 'skills' and toolkits that let Claude Code, Codex and other coding agents generate or edit video: rendering frameworks like HyperFrames and Remotion, motion graphics, explainer/promo video generators, short-form editors, digital avatars and music videos. Each entry is read and security-graded by a companion service (Agent Skills Hub / agentskillshub.top), with a machine-readable JSON feed and category breakdowns (frameworks, promos, explainers, editing, shorts, avatars, animation, motion graphics, scripts, music videos).
github.comrepoAdded 29 Sep 2026, published 27 Sep 2026🧠 AI - 0xtbug/Recat
Recat is a local, Bun-based web workspace for reviewing security findings, including ones produced by AI agents such as Hermes, Codex and Claude Code. It reads a folder of finding.json, README and PoC evidence per project, and offers a dashboard by severity, status and asset coverage (web, smart contract, mobile, desktop, network, hardware). It also has filters by vulnerability class, an evidence viewer, JSON and ZIP exports, password-protected access with a censored view, and a SKILL.md reporting skill that lets agents write findings straight to the source folder.
github.comrepoAdded 16 Oct 2026, published 27 Sep 2026🛡️ Security - Agent Control Standard (ACS)
Agent Control Standard (ACS) is an OWASP GenAI Security Project specification that lets a separate Guardian Agent inspect an AI agent's proposed actions before they execute and return allow/deny/modify/ask/defer over an authenticated JSON-RPC wire, with OpenTelemetry/OCSF audit trails and a CycloneDX/SPDX/SWID AgBOM inventory. The reference implementation runs Microsoft's Agent Governance Toolkit (AGT) behind the ACS contract with Bun, including host shims for Claude Code and OpenCode, and demonstrably denies a destructive `rm -rf /` command from a live coding-agent session while allowing benign ones. The project is explicit about current gaps — the wire is unauthenticated (issue #70) and the reference Guardian fails open by default (issues #32/#37) — and only 2 of 16 lifecycle hooks are evaluated live in v0.1.0.
github.comrepoAdded 26 Sep 2026🛡️ Security - FirmAgent: Fuzzing + LLM Agents for IoT Firmware Vulnerability Discovery (NDSS 2026)
FirmAgent is an academic research toolkit (NDSS 2026) for finding vulnerabilities in re-hosted IoT firmware web services by combining IDA-based pre-fuzzing (CFG/sink distance scoring), QEMU instrumented tracing, CFG-guided API fuzzing, and an optional LLM agent (LLMATaint.py) that consumes runtime taint traces to reason about and produce PoCs for bug classes like command injection. The pipeline is explicit about scope: it is meant for authorized, owned or re-hosted firmware (e.g. Greenhouse-style containers), and stitches together sink-scope extraction, feedback-driven fuzzing, and request-to-trace attribution before handing traces to an LLM for taint-to-PoC analysis.
github.comrepoAdded 26 Sep 2026🛡️ Security - SAPMAP — SAP Landscape Attack Path Mapper
SAPMAP is a BloodHound-style attack path mapper for SAP landscapes: it discovers SAP systems on a network, maps RFC trust connections, and implements real exploits (10KBLAZE/CVE-2020-6207 gateway trust, CVE-2025-31324 VisualComposer JSP webshell, a described CVE-2026-58240 Message Server rogue-registration flaw, and CVE-2026-31431 root LPE via AF_ALG page-cache patching) to chart lateral movement across ABAP, Java, HANA, and BTP-connected systems. Its AutoPwn mode chains scan → exploit → enrich → propagate across an entire landscape, and it includes an engagement-report generator, SecStore/RSECTAB credential decryption, SSH lateral movement, hash cracking via hashes.com, and a Tier-3 "evasion" module (SAL slot disable, DBTABLOG purge) paired with an extensive, specific blue-team detection guide (SAL/SM20, DBTABLOG gaps, kernel-param diffing, OS/network IOCs) for defenders to catch it.
github.comrepoAdded 26 Sep 2026🛡️ Security  MiMo-V2.6-Flash-RL (Xiaomi)
MiMo-V2.6-Flash-RL is Xiaomi's efficiency-balanced checkpoint in the MiMo-V2.6 series, a 309B-total/15B-activated sparse MoE model with native text, image, video and audio support and a 1M-token context window. It's trained with a single mixed reinforcement learning run (GRPO at large batch scale) across coding, agentic, visual and cybersecurity tasks, using a novel Groupwise Agentic Grading scheme (Groupwise Reward Synthesis and Groupwise Advantage Redistribution) to build a self-improvement loop, followed by Multi-Prefix Multi-Teacher On-Policy Distillation (MOPD2). The card documents the architecture (MiMo ViT vision encoder, AudioTokenizer audio encoder, 5-layer speculative MTP decoder) and deployment recipes for vLLM and SGLang.
huggingface.corepoAdded 26 Sep 2026🧠 AI- garak v0.17.0 — adds EU AI Act risk-category mapping
garak is NVIDIA's open-source LLM vulnerability scanner that runs probes/detectors for jailbreaks, prompt injection, PII leakage, package hallucination, markdown exfiltration and more against LLM targets. This v0.17.0 release adds a new EU AI Act risk-category mapping to tag and group probe results by the Act's risk categories, alongside fixes to the agent_breaker judge, markdown-exfiltration detectors, Ollama auth/generation support, and dropped Python 3.10 in favor of 3.13 support.
github.comrepoAdded 26 Sep 2026🛡️ Security - Agent Threat Rules (ATR) — open detection-rule standard for AI agent threats
Agent Threat Rules (ATR) is an open, versioned YAML rule format (ATR-YYYY-NNNNN scheme) for detecting AI-agent runtime threats — prompt injection, tool-poisoning, malicious SKILL.md content, and MCP exchange abuse — evaluated by a reference TypeScript engine (with a Python wrapper) shipped as an npm/pip package, CLI, GitHub Action, and Docker scanner with SARIF output. The project positions itself as "Sigma for agent threats," maps rules to OWASP Agentic/LLM Top 10, MITRE ATLAS, and NIST AI RMF, and publishes an extensive (and unusually self-critical) benchmark suite against corpora like garak, PromptBench, and PromptInject, including documented harness bugs and withdrawn recall figures.
github.comrepoAdded 26 Sep 2026🛡️ Security - MITRE ATLAS v2026.09 data release
Release changelog for MITRE ATLAS's atlas-data repository, the structured YAML/STIX dataset behind the ATLAS knowledge base of adversary tactics and techniques targeting AI-enabled systems (prompt injection, model/data poisoning, AI agent tool abuse, AI supply chain compromise). The v2026.09 release brings the matrix to 120 techniques, 88 sub-techniques, 40 mitigations, and 73 case studies, and recent versions introduced a new v6 YAML data format with Pydantic/SQLAlchemy/FastAPI tooling, platform tagging (Predictive AI, Generative AI, Agentic AI, Enterprise), and renamed/generalized techniques like "AI Agent Tool Poisoning," "Manipulate AI Model," and "Enterprise Resource Discovery." It's the canonical, actively-maintained taxonomy practitioners use for AI red-teaming, threat modeling, and mapping real-world AI attack case studies.
github.comrepoAdded 26 Sep 2026🛡️ Security - awslabs/mcp release 2026.09.20260922000649
This is a release changelog for awslabs/mcp, AWS Labs' collection of Model Context Protocol servers covering services like HealthOmics, Aurora DSQL, Bedrock Knowledge Base retrieval, ECS, CloudWatch, billing/cost management, and dataprocessing. This release adds vended metrics tools, SQL parser-based policy guards for Aurora DSQL, agentic retrieval support for Bedrock KB, and fixes several security issues including region validation to prevent SSRF credential disclosure in the CloudWatch server and read-only mode bypass in the MySQL server. It reflects an actively maintained, high-velocity multi-server MCP monorepo used for AWS tool integration with LLM agents.
github.comrepoAdded 26 Sep 2026🧠 AI - dzhng/jevgrep
Jevgrep (the `jg` CLI) lets a coding agent ask a natural-language question about a repository and get back relevant files, reading leads, and verbatim source excerpts in one response, using an LLM (Jev) to judge relevance across folders, files, and declarations instead of relying on grep/ripgrep alone. It ships an installable "skill" for Claude Code, Codex, OpenCode and other agents that teaches them when to call jg versus their normal tools, and requires a key for Vercel AI Gateway, TypeSafe, OpenRouter, or OpenCode Zen. A reported ten-task SWE-bench repeat found ~40% lower coding-agent cost ($7.62 to $4.52) but a lower solve rate (7/10 vs 8/10 baseline), explicitly framed as a cost/quality tradeoff rather than a win.
github.comrepoAdded 27 Sep 2026, published 26 Sep 2026🧠 AI - graygnatconsole/mcp-audit-tool
mcp-audit-tool is a dependency-light Python CLI that statically scans Claude Desktop, Cursor, Windsurf, Cline, Zed, and VS Code MCP configuration files for security issues, including hardcoded secrets, unpinned/rug-pull packages, pipe-to-shell installers, tool-poisoning via hidden instructions in tool descriptions, filesystem servers rooted at '/', and unauthenticated plaintext HTTP MCP endpoints. It auto-discovers configs across macOS/Linux/Windows, produces a security score/grade plus SARIF 2.1.0 output for GitHub Code Scanning, and is built around the OWASP MCP Top 10 categories with a CI/CD example that fails builds on severity thresholds. The roadmap adds live server probing over stdio/SSE for runtime rug-pull detection and an ML-based prompt-injection classifier for tool descriptions.
github.comrepoPublished and added 26 Sep 2026🛡️ Security - Sandyaa — open-source autonomous code auditor that proves bugs with working exploit PoCs
Sandyaa is an open-source autonomous code-audit tool that points at a local directory or git URL and runs end-to-end, driven by the Claude Code CLI (optionally Gemini) with no separate API key required. It uses a Recursive Language Model approach — the model drives a Python REPL to chunk code, spawn sub-LLM queries, and aggregate results — running eight recursive passes (call-chain tracing, data-flow expansion, vulnerability chaining, exploitability proof, etc.) and an attacker-control-reachability analyzer to filter unreachable findings, then writes each finding with a working exploit PoC and an evidence.json linking claims to file/line. Maintained by SecureLayer7, who report using it to surface zero-days; it's alpha-stage, macOS-tested, Linux/WSL2-expected-to-work, and unsupported on native Windows.
github.comrepoAdded 26 Sep 2026🛡️ Security - MCP Python SDK v2.2.0
Release notes for MCP Python SDK v2.2.0, the reference Python implementation of the Model Context Protocol. Key changes: HTTP client redirects are now restricted to the same origin as the endpoint, idle Streamable HTTP sessions expire after 30 minutes (with a 10,000-session cap), OAuth authorization server metadata issuer checks are now enforced on the legacy discovery path, and new deprecation warnings push toward requiring explicit `issuer=` and `validate_token_resource` settings ahead of a 3.0 release.
github.comrepoAdded 26 Sep 2026🧠 AI  Ling-3.0-flash-VL (InclusionAI/Ant Group)
Ling-3.0-flash-VL is InclusionAI/Ant Group's native multimodal model built on Ling-3.0-flash, adding image and video understanding via a ViT encoder, VideoRoPE, and a hybrid MoE backbone (42 layers alternating KDA and Gated MLA at 5:1) with 124B total parameters but only 5.5B activated per token, and a 256K context window. It targets agentic multimodal workflows — understanding, reasoning, and acting on visual interfaces — scoring 42 on Artificial Analysis Intelligence Index v4.1.1, up from 38 for the text-only Ling-3.0-flash. The card includes concrete SGLang and vLLM serving recipes for various GPU configurations.
huggingface.corepoAdded 26 Sep 2026🧠 AI- google/ax — declarative agentic orchestration runtime
AX is Google's declarative orchestrator for running large numbers of autonomous agent workloads on Kubernetes, built on top of "Agent Substrate" for sandboxed execution. Agents are declared via YAML manifests (Task, Workspace, Model) similar to kubectl, and applied with an `ax` CLI that supports apply/get/watch/ssh/suspend/resume, treating agent runs as a distinct workload type distinct from stateless services or batch jobs.
github.comrepoAdded 26 Sep 2026🧠 AI - Hindsight — Agent Memory That Learns
Hindsight is an open-source agent memory system (MIT-licensed, self-hostable via Docker/Helm or usable as Hindsight Cloud) that goes beyond RAG-style recall by having agents learn through consolidated observations and mental models built from retained facts and experiences. It exposes retain/recall/reflect operations, a built-in MCP server per memory bank, Python/Node/Go/CLI clients, an LLM-wrapper for drop-in memory on OpenAI/Anthropic calls, and reports state-of-the-art results on the LongMemEval long-term memory benchmark, independently reproduced by Virginia Tech's Sanghani Center and The Washington Post.
github.comrepoAdded 26 Sep 2026🧠 AI - rewanthtammana/Who-Let-The-Agents-Act
who-let-the-agents-act is a self-hostable lab suite (Docker/Python, Groq-backed LLM agent) with nine isolated scenarios — overpowered data tools, IDOR-style cross-account access, unsafe agent handoffs, refund-limit bypass, indirect prompt injection via poisoned invoices, multi-tenant RAG leakage, secret leakage through debugging, fail-open approval outages, and a multi-hop confused-deputy agent chain. Each scenario runs in multiple modes (vulnerable vs. application-enforced) against the same prompt, recording model plan, policy decision, tool calls, and DB access as JSON so a reader can directly compare what changes when authorization is enforced outside the system prompt.
github.comrepoAdded 26 Sep 2026🛡️ Security - Chocapikk/CVE-2026-21858
A GitHub PoC chaining two n8n CVEs into unauthenticated RCE: CVE-2026-21858 abuses a Content-Type confusion in the Form Trigger/Respond-to-Webhook nodes to read arbitrary files (e.g. /proc/self/environ, the SQLite database, and the config file), from which the attacker derives the JWT secret from n8n's encryptionKey and forges an admin session cookie. That admin access is then used to create a workflow exploiting CVE-2025-68613, an expression-injection sandbox bypass (`this.process.mainModule.require`) that yields command execution, all demonstrated with a working Python exploit script and Docker lab against n8n 1.65.0. It notes the exploit was developed independently of a prior Cyera/Dor Attias write-up on a related n8n chain and details the specific vulnerable workflow pattern (file-upload form + binary Respond node) required for exploitation.
github.comrepoAdded 26 Sep 2026🛡️ Security - AgentSystemLabs/agent-office
agent-office is an open-source Node.js application that renders your team's projects as floors of a cartoon 3D office, where each Claude Code, OpenCode or Codex coding-agent worker sits at a desk with a visible terminal others can join. It wires agent workers directly into GitHub: an issues board and PR board with diff review, CI status and merge actions, a task queue that auto-hires workers into isolated git worktrees, one-click PR creation, live worker status via Claude Code/Codex hooks and an OpenCode plugin, and per-worker cost/token tracking against Claude plan limits. It also supports multi-agent meeting-room collaboration patterns such as debate, lead and team, map-reduce, red and blue, and review panel, where several agent workers jointly produce a file and open a PR, plus shared voice chat and screen sharing for the human team.
github.comrepoAdded 28 Sep 2026, published 26 Sep 2026🧠 AI - git-pkgs — dependency history & supply-chain analysis for git repos
git-pkgs is a Go rewrite of a Ruby tool that adds a git subcommand for tracking dependency changes across a repository's history, indexing manifests/lockfiles from 36+ package managers (npm, RubyGems, Cargo, PyPI, Maven, Composer, Go modules, etc.) into a local SQLite database. Beyond history/blame/diff, it offers supply-chain security commands: `vulns` (OSV-based CVE scanning with SARIF output for GitHub code scanning, plus blame/praise/exposure for remediation metrics), `licenses` (with drift detection and CI-friendly exit codes), `deprecated`, `provenance` (trusted-publishing/attestation checks), `integrity` (lockfile hash drift detection), `maintainers`/`health` (via ecosyste.ms metadata), and `sbom` export in CycloneDX/SPDX. It also supports a dependency-aware `bisect` to find when a vulnerability, license change, or capability (e.g. network access) was introduced, and ships GitHub Actions for CI integration.
github.comrepoAdded 25 Sep 2026🛡️ Security - respanai/respan-gateway
respan-gateway is an open-source Rust LLM gateway shipped as a single binary with a built-in web UI. It lets OpenAI Chat Completions, Responses, Anthropic Messages and Gemini generateContent clients call any model, translating tools, images and reasoning. It adds named routes, fallback, retries, hedged races, MCP server fronting, per-call pricing, request logs and plugins.
github.comrepoAdded 22 Oct 2026, published 25 Sep 2026🧠 AI - Claude Code Templates Repository
Claude Code Templates (aitmpl.com) is an open-source npx CLI and template catalog offering 100+ ready-to-use agents, slash commands, hooks, settings, skills and MCP server integrations for Anthropic's Claude Code, aggregating contributions from Anthropic's official skills repo, K-Dense-AI's scientific skills, and various community projects (superpowers, wshobson/agents, awesome-claude-code, etc.). Beyond the template catalog it ships real-time analytics for monitoring Claude Code sessions, a mobile chat viewer with Cloudflare Tunnel support, a health-check diagnostic, and a plugin/marketplace manager, making it a practical operational toolkit for customizing and running Claude Code.
github.comrepoAdded 2 Oct 2026, published 25 Sep 2026🧠 AI - https://github.com/davila7/claude-code-templates/tree/main/cli-tool/components/skills/security/security-threat-model
A directory within the davila7/claude-code-templates repo containing a "security-threat-model" Skill for Claude Code: a SKILL.md instruction file plus supporting agents and reference files that package a reusable threat-modeling workflow for the coding agent. It's an example of the emerging pattern of distributing structured, invocable skills (instructions + sub-agents + reference docs) that extend Claude Code's capabilities, rather than a security research artifact itself.
github.comrepoAdded 2 Oct 2026, published 25 Sep 2026🧠 AI - https://github.com/davila7/claude-code-templates/tree/main/cli-tool/components/skills/security/security-threat-model
A "security-threat-model" skill folder in the davila7/claude-code-templates repository, part of a library of reusable Claude Code skills/components. It packages a SKILL.md definition with supporting agent and reference files intended to let Claude Code agents carry out structured threat-modeling analysis as part of a development or security-review workflow.
github.comrepoAdded 2 Oct 2026, published 25 Sep 2026🛡️ Security - Show HN: Whiteboard (YC W26) – An open-source IDE for thoughtful software design
Whiteboard is an open-source (MIT) desktop IDE that gives coding agents like Claude Code and Codex an SDK to draw diagrams, sequence charts, and traces on a shared canvas linked directly to underlying code. It vendors Code OSS for VSCode-grade navigation/LSP support and adds a custom Rust-built AST-aware semantic diff viewer (with a WASM plugin system) that summarizes large generated functions as pseudocode and collapses noise like tests/docs, aiming to make reviewing autonomous agent decisions and code changes tractable.
github.comrepoAdded 26 Sep 2026, published 24 Sep 2026🧠 AI - yetone/magpie
magpie is a cross-platform menu bar app, TUI and CLI that lets you view and switch the model each installed AI coding agent (Claude Code, Codex, Gemini CLI, OpenCode, Cursor, Copilot CLI, Goose, Pi, etc.) is configured to use, editing each agent's config file surgically without disturbing comments or formatting. It runs a local gateway (127.0.0.1:3425) that translates between OpenAI Chat Completions, OpenAI Responses and Anthropic Messages APIs so every agent can point at one endpoint and use any provider's models, including routing groups that spread requests across multiple keys/subscriptions with configurable routing strategies (smart, order, rotate, usage). It can also reuse existing subscriptions (Claude Code, Codex/ChatGPT, Copilot, Devin, Gemini CLI) as providers for other agents without exposing or copying credentials, and supports encrypted profile backup/restore.
github.comrepoAdded 26 Sep 2026, published 23 Sep 2026🧠 AI - artemy-ccrsky/COM-Jungle
COM-Jungle is a GitHub repository of offensive security research notes on Windows COM (Component Object Model), written by Artemy Tsetsersky in 2026. Notes are ordered by tactic: how COM works, execution, trust boundaries and privilege escalation, lateral movement via DCOM, persistence, initial access, finding new classes, and detection and hardening. It advises recording build, bitness, token and session before generalising a CLSID result, and says detections should key on registration, load and process context rather than a single CLSID.
github.comrepoAdded 23 Oct 2026, published 23 Sep 2026🛡️ Security - https://github.com/akha-security/akca
AKCA is an open-source, Go-based Dynamic Application Security Testing (DAST) scanner that combines HTTP and headless-browser crawling, JavaScript/AST analysis, API spec import (OpenAPI, GraphQL, gRPC, etc.), and adaptive active testing across a very broad set of vulnerability classes including SQL injection, XSS, SSRF, IDOR/BOLA, SSTI, JWT/OAuth flaws, race conditions, and cloud/CI exposure. It emphasizes evidence-oriented verification — replaying promising signals against baselines, negative controls, and OAST callbacks before promoting them to findings — and exports Burp-style HTTP evidence in HTML, JSON, CSV, Markdown, and SARIF reports. Positioned as a transparent, single-developer alternative inspired by but not claiming parity with Acunetix, Invicti/Netsparker, or Burp Suite Professional.
github.comrepoAdded 2 Oct 2026, published 23 Sep 2026🛡️ Security - shai-hulud-detect: multi-ecosystem npm/PyPI/Composer/Crates/Go/Hex/RubyGems supply-chain worm scanner
shai-hulud-detect is a dependency-free Bash scanner that checks projects against a 5,782-entry list of compromised npm, PyPI, Composer, Crates, Go, Hex, and RubyGems package versions, plus content-pattern indicators of compromise (malicious file hashes, C2 domains, dead-man's-switch artifacts, forged commits, suspicious lifecycle hooks) tied to the Shai-Hulud supply-chain attack waves. It supports single-project and bulk scanning, CI-friendly exit codes, JSON/log output for pipeline gating, and a --check-host mode to detect the May 2026 gh-token-monitor/kitty-monitor persistence daemons that wipe hosts if their monitored GitHub token is revoked (with a documented safe remediation order). Detection is read-only; new package entries are sourced from named threat-research firms (Socket, StepSecurity, Aikido, Snyk, JFrog, Wiz, Semgrep, SafeDep, GitGuardian, OX Security) and cited in PRs.
github.comrepoAdded 23 Sep 2026🛡️ Security - nealbridges/VulnHunter
VulnHunter is a maintained fork of Capital One's open-source agentic security scanner, reworked to run on any agent harness (Claude Code, Codex, Grok/OpenCode) instead of being Claude-Code-specific. The fork's distinguishing work is engineering, not security findings: portable "skill" prompt files with an explicit environment contract, an installer that fails loudly instead of guessing paths, Docker-based sandboxed exploit validation, and a benchmark harness that ran six full scans of one production Go service across five model/harness stacks, finding that result counts swung from 3 to 42 findings depending on how rigorously exploits were validated. It ships three composable skills (/vulnhunt, /vulnhunter-fix, /vulnhunt-fix-verify), a headless batch-runner (harness/), and a deterministic manifest-writing CLI (vh).
github.comrepoAdded 6 Oct 2026, published 22 Sep 2026🧠 AI - nealbridges/VulnHunter
A maintained, harness-portable fork of Capital One's open-source VulnHunter — an agentic AI tool that performs attacker-first forward analysis on source code to find exploitable vulnerabilities, falsify weak findings, and produce evidence-backed PoCs rather than pattern-matched SAST alerts. This fork adds containerized (Docker-based) exploit validation, measured-impact PoCs (rows leaked, amplification factor, etc.), and portability across agent harnesses (Claude Code, Codex, Grok, etc.) via environment-contract prompt files, plus an unattended operator (vulnhunter-run) and batch-scanning/benchmark harness tested against OWASP NodeGoat, Juice Shop, and WebGoat.
github.comrepoAdded 6 Oct 2026, published 22 Sep 2026🛡️ Security - qybaihe/mu
mu is a coding agent built on the pi framework that introduces a "judgment kernel": a small, fast auxiliary model (Jev, a hosted judge, or Laya, a local 322M-parameter model) answers bounded yes/no/choice/score questions at 35 named decision points per turn — deciding what stays in context, whether a tool call is risky, when a turn is done, and what one agent should tell another — so the large working model doesn't spend tokens/attention on bookkeeping. It also ships a "hive" multi-agent mode (2-6 read-only "bees" plus a main editing agent) with an append-only shared board and relation-checking (supersedes/contradicts/supports) between findings, plus a native desktop app with live judgment/board/hive views.
github.comrepoAdded 26 Sep 2026, published 22 Sep 2026🧠 AI - DVLAA
DVLAA (Damn Vulnerable LLM and Agent Application) is a self-hosted, Docker-deployable security training range for LLM and agent applications, modeled on the DVWA concept but for AI. It covers OWASP LLM Top 10 and Agent Security Top 10 risks (prompt injection, RAG poisoning, tool abuse, memory poisoning, excessive resource consumption, etc.) through 81 hands-on challenges, including an "AWDP" attack/defense track where 10 challenges reproduce real disclosed vulnerabilities in Dify, RAGFlow, Langflow, Flowise, Open WebUI and n8n (with optional real upstream container reproduction), 20 challenges adapted from a China–ASEAN AI security CTF, and 6 challenges adapted from a real model-poisoning CTF. It provides real model interaction, state-machine flag verification, source/prompt viewers, model management (local, Ollama, SiliconFlow, OpenAI-compatible), and bilingual UI.
github.comrepoAdded 22 Sep 2026🛡️ Security - yibie/jev-engineering-zh
A Chinese translation (with original source notes) of a design essay synthesizing TypeSafe founder Diogo Almeida's notes on 'Jev,' a typed decision model that drives a coding-agent harness. It argues coding agents are simple loops whose real leverage lies in how context is assembled each turn, and works through six problems inherited from KV-cache-driven, append-only context design: costly model routing, tool-schema bloat, lossy compaction, rare sub-agents, destructive session restarts, and the built-in-capabilities tradeoff. It proposes fixes including query-aware context scoring/visibility tiers, cost-aware routing that accounts for cache reprocessing, tiered tool disclosure, conditional AGENTS.md loading, and shared read-only background retrieval.
github.comrepoAdded 26 Sep 2026, published 22 Sep 2026🧠 AI - Supply Chain Firewall (Datadog)
Supply Chain Firewall (SCFW) is a Datadog-built CLI that wraps npm, pip, and poetry commands to inspect every package target against known-malicious/compromised package datasets (the open-source malicious-software-packages-dataset and OSV.dev) before installation proceeds, blocking or warning on hits. It ships as a single Go binary, can be aliased transparently into a developer's shell, and optionally reports run outcomes and enforces centralized allow/block policies through Datadog Code Security across a fleet, sending only package metadata (never source code) to Datadog.
github.comrepoAdded 22 Sep 2026🛡️ Security - Show HN: Foremerge – Catch intent conflicts between parallel coding agents
Foremerge is an open-source coordination protocol layered above Git for parallel coding agents (Claude Code, Codex, Cursor). Agents publish semantic intent (scopes like symbol/api/schema) before editing into a shared SQLite store under .git, so Foremerge can detect intent conflicts—like one agent replacing a class another is extending—that Git's text-diff merging would silently miss. It's advisory-only (no file locking), deterministic (no LLM judgment calls), and gates ChangeSet acceptance on Foremerge-run validation rather than agent self-reports.
github.comrepoAdded 26 Sep 2026, published 21 Sep 2026🧠 AI - merijjeyn/jive
Jive is an open-source agent framework that replaces the standard LLM-call/tool-call loop with 'Graph Calls' — DAG-based workflows combining traditional tool calls with fast 'Jev' (System One) model calls for repetitive or intuitive steps. It aims to reduce token cost and latency versus agents like Claude Code and Codex by only invoking expensive reasoning LLM calls when needed, letting cheaper System One models follow through on planned execution graphs.
github.comrepoAdded 26 Sep 2026, published 21 Sep 2026🧠 AI - Simreal-AI/Simreal-MLBench
Simreal-MLBench is the open, minimal slice of ML Benchmark, a verifiable evaluation environment for machine learning research agents, covering 60 tasks across tabular learning, forecasting, vision, language, audio, multimodal and structured scientific data. It splits an open, Apache-2.0 layer (task definitions, scoring rule, verification tooling) from a commercial operated layer (SimReal's sandboxed runtime, gateway, submission broker and official scoring), scores tasks as 100xp^2 against a frozen reference leaderboard, enforces a source-blind two-submission protocol, and provides full provenance for every published number. It is positioned as an alternative to MLE-bench with a distinct task selection, resource protocol, and scoring scheme, aimed at supporting RLVR and agent self-improvement research.
github.comrepoAdded 26 Sep 2026, published 21 Sep 2026🧠 AI - StellarFoundry/soroban-security-scanner
soroban-scan is an open-source, deterministic static analyzer for Stellar Soroban smart contracts and Rust projects. It ships 19 Soroban-aware detectors (SS-001 to SS-033) covering missing authorization, re-initialization, cross-contract call ordering, unchecked arithmetic and storage or resource misuse. Output includes JSON, SARIF 2.1.0 and GitHub annotations, with baselines and a PR-scanning Action. The project describes itself as early development.
github.comrepoAdded 28 Oct 2026, published 21 Sep 2026🛡️ Security - SnailSploit/Claude-Red
claude-red is a GitHub library of structured SKILL.md files for the Claude Skills system, each priming Claude with expert-level offensive-security methodology for a specific attack surface (SQL injection, shellcode, EDR evasion, ADCS abuse, wireless, IoT, cloud, mobile, fuzzing, etc.). Skills load on-demand from conversational triggers so context isn't spent on unused domains, and can be installed wholesale, per-category via sparse-checkout, or pasted directly into a system prompt. It's aimed at authorized red-team engagements, bug bounty triage, CTF prep, and operator training, building on Sahar Shlichov's offensive checklist collections.
github.comrepoAdded 21 Sep 2026🛡️ Security - Lonkero — Rust web vulnerability scanner (v3.7, AI agent mode)
Lonkero is an open-source Rust web vulnerability scanner (v3.7) combining 125+ context-aware scanners with an AI agent mode that drives targeted scans via natural-language conversation (using Claude, GPT, or local Ollama models). Notable techniques include a browser-free "proof-based" XSS engine that mathematically proves exploitability from reflection context + escape behavior, an "OOBZero" engine for detecting blind SQLi/SSRF/XXE via Bayesian multi-channel statistical inference and Pearson-correlated timing attacks without external callback infrastructure, Next.js middleware-bypass detection (CVE-2025-29927, CVE-2024-34351), AWS Cognito user-enumeration checks, and a scanner module that detects invisible prompt-injection payloads hidden in README.md files targeting AI coding assistants.
github.comrepoAdded 21 Sep 2026🛡️ Security - CVE-2026-26980 — Ghost CMS Content API unauthenticated blind SQLi lab
A Docker-based exploitation lab for CVE-2026-26980, an unauthenticated blind SQL injection in Ghost CMS's Content API (versions before 6.19.1). The bug lives in slug-filter-order.js, where slug values from the array-notation filter syntax (filter=slug:['value']) are interpolated unsanitized into an ORDER BY CASE statement, letting NQL's single-quote-wrapped literals smuggle raw SQL past input validation; since MySQL treats || as OR and empty strings as falsy, attackers get a clean boolean oracle to extract data (e.g. admin email/password hash) from any Ghost site using only the publicly embedded Content API key. The repo includes exploit.py for full setup/verify/extract, a docker-compose lab spinning up both vulnerable (6.18.0) and patched (6.19.1) Ghost instances, and also mentions a second patched bug (jsonpath/static-eval prototype pollution in the {{#get}} Handlebars helper leading to RCE via themes).
github.comrepoAdded 21 Sep 2026🛡️ Security - watchTowr detection artifact generator for Splunk CVE-2026-20253
A Python script from watchTowr Labs that checks whether a Splunk Enterprise instance is vulnerable to CVE-2026-20253, a pre-auth RCE stemming from unauthenticated access to the PostgreSQL Sidecar Service's /v1/postgres/recovery/backup endpoint. It probes the endpoint and reports vulnerable/not-vulnerable based on the HTTP response code, without performing actual exploitation. Affected versions span Splunk Enterprise 10.0.0–10.0.6 and 10.2.0–10.2.3; 10.0.7, 10.2.4, and 10.4.0 are patched.
github.comrepoAdded 21 Sep 2026🛡️ Security - awarexone/Agentic-Bug-Hunter
Agentic-Bug-Hunter is an open-source CLI (bughunter) and Claude Code plugin that automates the bug bounty pipeline end-to-end: recon, vulnerability hunting across 26 web2 and 10 web3/smart-contract bug classes, a "7-Question Gate" validation step to kill weak findings, and submission-ready report generation for HackerOne, Bugcrowd, Intigriti, and Immunefi. It orchestrates existing scanners (subfinder, httpx, nuclei, katana, ffuf, dalfox) behind a multi-provider LLM layer (Ollama, Groq, DeepSeek, Claude, OpenAI) and cross-session "hunt memory," and also ships an MCP server for use from Cursor, Codex, or OpenCode.
github.comrepoAdded 21 Sep 2026🛡️ Security - Gihchathur/kubemotion
KubeMotion is a browser-only visualizer that turns raw Kubernetes YAML or a packaged Helm chart (.tgz) into an interactive, Argo CD-style dependency graph without ever connecting to a live cluster or executing Helm. Beyond visualization it runs rule-based checks for common deployment problems — missing probes, incomplete containers, missing selectors, missing service accounts, and mutable image tags — surfaced per-resource in an inspector panel, and can export the resulting architecture as a Mermaid diagram. Built with React, TypeScript, Vite, React Flow and CodeMirror; explicitly a read-only, credential-free tool for reviewing manifests/charts before they're applied.
github.comrepoAdded 21 Sep 2026🛡️ Security - ossf/criticality_score
criticality_score is an OpenSSF tool that computes a 0-1 criticality score for open source projects (based on an algorithm by Rob Pike), using signals like contributor count, commit frequency, dependents count, and org diversity to identify projects the ecosystem critically depends on. It ships a CLI, config files for tuning scoring weights, and companion tools (enumerate_github, collect_signals, scorer) for large-scale data collection; the project's GCP-hosted BigQuery/GCS datasets will be discontinued after 2026-08-29, with data moving to a static data directory.
github.comrepoAdded 21 Sep 2026🛡️ Security - zai-org/ZCode
ZCode is an AI programming workbench (from zai-org) providing a desktop Electron app, a browser-based Web UI, and a terminal Agent CLI and TUI, all backed by a shared backend and Agent runtime. The repo includes build and dev scripts for bootstrapping the monorepo, running desktop and web dev modes, and packaging a unified zcode CLI binary that can launch either a TUI or a local web server hosting the same agent backend.
github.comrepoAdded 26 Sep 2026, published 20 Sep 2026🧠 AI - Show HN: CUA-S1 – A System One Model for Computer Use
Cua is an open-source platform for computer-use agents: isolated cloud desktops (Fleets), a Sandbox SDK, local macOS/Linux VM management (Lume), a Cua Driver for controlling native apps/browsers via CLI/MCP/SDKs, and Cua-Bench for building and evaluating computer-use tasks. It also introduces CUA-S1, a family of small specialized "System 1" models that make fast, bounded decisions (e.g., scoring form field values from structured UI/document data) rather than generating agent actions token-by-token, with the first CUA-S1-FORMS model and dataset released on Hugging Face. The project is MIT-licensed with some optional components (cua-som, cua-perception's OmniParser integration) carrying AGPL-3.0 obligations.
github.comrepoAdded 26 Sep 2026, published 19 Sep 2026🧠 AI - sno-ai/sno-station
Sno Station is an open-source (Apache-2.0) local workstation that coordinates multiple AI agents (Claude Code, Codex, OpenClaw) as a 'Duo': they share an encrypted on-disk memory store, hand off tasks when one hits a rate limit, peer-review each other's work, and run a nightly self-improvement loop that proposes edits to their own skill files based on session history. It reports results on the Memora benchmark (FAMA/FAA metrics for forgetting-aware long-term memory) and cites Karpathy's 'LLM Wiki' and Google's WikiSkill as design inspirations.
github.comrepoAdded 26 Sep 2026, published 19 Sep 2026🧠 AI - Shor
Shor is a source-available, multi-tenant autonomous pentesting platform where a ~17-agent LLM pipeline (discovery, hypothesis, adversarial screening jury, exploitation, proof replay) attacks a target URL and optionally its connected source repo. It wields 30+ real offensive tools (sqlmap, dalfox, nuclei, jwt_tool, hydra, ffuf, etc.) plus SAST/secret/SCA tools (Semgrep, Gitleaks, TruffleHog, OSV-Scanner, Trivy) in white-box mode, and only reports findings whose PoC is deterministically re-executed and confirmed by a code-enforced safety layer under a signed Rules of Engagement, with scan authorization gated behind single-use human-minted tokens on its MCP/automation surface.
github.comrepoAdded 22 Sep 2026, published 19 Sep 2026🛡️ Security - Outrider Recon
Outrider Recon is an open-source, Claude-native multi-agent OSINT and external attack-surface recon platform for authorized engagements, covering web/API, identity/SSO, cloud, secrets, and people/breach intelligence. It deliberately stops short of exploitation: active enumeration is approval-gated and intrusive validation is a human hand-off, with deterministic Python controls enforcing scope, evidence integrity, workflow state, and finding promotion around Claude skills and optional MCP-based enrichment. Output is ranked, evidence-backed finding cards (confidence/severity/handoff recommendations) meant to feed proxy-assisted testing or pen-testing rather than raw scanner dumps.
github.comrepoAdded 22 Sep 2026, published 19 Sep 2026🛡️ Security - kerpopule/hermes-jev-skills
hermes-jev-skills wires TypeSafe's small, fast decision model "Jev" into agent workflows (Hermes, Claude Code, Codex) to handle cheap sub-decisions — which model should answer a turn, which of many skills to load, which retrieved passages matter, which conversation turns survive a summary — instead of burning frontier-model tokens on them. It ships ten agent-agnostic SKILL.md files, a CLI (jev routing/mail/screen/search), a local dashboard, and a plugin built on public Hermes seams (pre_llm_call, transform_tool_result, llm_request middleware) with detailed data-redaction guarantees for what gets sent to the Jev API. It also includes a shadow mode for safely evaluating routing decisions before enabling them.
github.comrepoAdded 26 Sep 2026, published 18 Sep 2026🧠 AI - vinilana/jev-gateway
jev-gateway is a local proxy that sits between coding agents (Codex, Claude Code, OpenCode, Kilo, Gemini CLI, Devin) and their LLM backend, intercepting only the tool-selection decision and routing it to TypeSafe's small, fast "Jev" model instead of the main reasoning model, while forwarding everything else untouched. It supports forced tool_choice, hint-based suggestions (for APIs like Anthropic's that can't force a tool mid-turn), a live dashboard for cost/latency/routing metrics, and a companion benchmark repo (jev-gateway-bench) showing routing helps most on debugging tasks but can hurt some models on feature-building tasks.
github.comrepoAdded 26 Sep 2026, published 18 Sep 2026🧠 AI - coldteadotai/abide
Abide is a CLI (npx @coldtea/abide) that hooks into Claude Code, Codex and OpenCode to check every agent edit or turn against project rules written in AGENTS.md/CLAUDE.md that a linter can't enforce (e.g. 'never let a raw error reach a user', 'no premature abstractions'). It uses Jev, TypeSafe's calibrated decision model, to answer a typed yes/no probability per rule per diff instead of a full LLM call, making it cheap (~300ms, fractions of a cent per turn) enough to check every edit; violations above a threshold are fed back to the agent to repair in the same turn.
github.comrepoAdded 26 Sep 2026, published 18 Sep 2026🧠 AI - Betterleaks — secrets scanner from the Gitleaks creator
Betterleaks is a configurable, fast secrets scanner maintained by the original Gitleaks author and team, capable of scanning git history, local filesystems, stdin, GitHub/GitLab orgs and specific PRs/MRs, Hugging Face models/datasets, and public S3/R2 buckets. Detection rules use regex plus an Expr (with legacy CEL compatibility) based prefilter/filter/validate pipeline, allowing entropy checks, keyword gating, and live API validation of found credentials (e.g. checking a GitHub PAT against api.github.com). It's used in production by projects like Aikido Security and shipped inside MegaLinter.
github.comrepoAdded 18 Sep 2026🛡️ Security - Tongyi-MAI/Qwen-Planner-Agent
Qwen-Planner-Agent is Alibaba's Tongyi MAI Team framework pairing a trained Planner Model with a stateful Harness to execute mobile tasks end-to-end, coordinating tools, persistent memory, reusable Skills, and sub-agents. It introduces Competence-Adaptive Reward-and-Advantage Engineering (CARE), a hybrid supervised+RL training approach, and reports the 27B model reaching 77.05% Overall on MobilePA-Bench at an estimated $2.41 per 1,000 tasks in output-token cost. This repo hosts the technical report/blog and recorded interactive examples rather than model weights or code.
github.comrepoAdded 26 Sep 2026, published 18 Sep 2026🧠 AI - Oldcircle/geo-sleuth
geo-sleuth is an open-source Agent Skill that lets any tool-using agent (Claude Code, Codex, Cursor, Gemini CLI, OpenCode, GitHub Copilot) geolocate a photo without relying on text, license plates or landmarks, instead using OpenStreetMap geometry, elevation data, satellite tiles and street view. It structures the task as a scored candidate board with ~20 single-purpose Python scripts (sun/terrain/osm/pose analysis, CLIP-ranked satellite matching, DINOv2+SIFT street-view matching) that do the ranking, while the LLM only judges among top candidates and must cite the command/file behind every claim. Output includes coordinates with an error radius, camera heading, and an evidence image.
github.comrepoAdded 26 Sep 2026, published 18 Sep 2026🧠 AI - OWASP Agentic Skills Top 10 (AST10)
The OWASP Agentic Skills Top 10 (AST10) is a new security framework cataloging the 10 most critical risks in AI agent "skills" — the behavior layer that orchestrates multi-step tool use in OpenClaw, Claude Code, Cursor/Codex, and VS Code. It documents real 2026 incidents (the ClawHavoc registry-poisoning campaign with 1,184 malicious skills, Snyk's ToxicSkills audit of 3,984 skills finding 36.82% flawed, CVE-2025-59536/CVE-2026-21852 RCE in Claude Code project files, and CVE-2026-28363 ClawJacked WebSocket hijacking) and proposes a Universal Skill Format (YAML) with signing, permission allowlists, and identity-file protections to mitigate them, mapped to CSA's MAESTRO 7-layer threat model.
github.comrepoAdded 18 Sep 2026🛡️ Security - PortSwigger/http-terminator
http-terminator is PortSwigger's AI-assisted research pipeline for finding and exploiting HTTP request-smuggling and response-desynchronization vulnerabilities. It chains four stages: seeker extracts desync vectors from RFCs and URLs, flamer generates malformed test cases, validator checks candidates against a live target via Burp Suite, and investigator exploits, confirms, and reports findings. Released under AGPL-3.0 as a reference companion to the underlying research, with explicit warnings to only run against authorized targets.
github.comrepoAdded 18 Sep 2026🛡️ Security - OmniJev/awesome-jev-gallery
An extensive, actively maintained GitHub "awesome list" cataloging the ecosystem that has grown around TypeSafe's Jev and its "System One" typed decision models — a non-generative alternative to chat LLMs that returns calibrated probabilities per option (Choice/Score/Noul primitives) via RLCD training and single-pass constrained decoding. It indexes dozens of open-weight reproductions (OneJev, Rizzo Flow, Laya, Jebadiah, kev), benchmarks and leaderboards (JevBench, Jev Decision Index, JevAdvBench, DecisionBench), downstream tools (browser/robot/trading agents built on the typed API), and the research lineage the design draws on (zero-shot entailment classifiers, InstructGPT's reward model, GLiNER/GLiClass, monoBERT, LLaDA, vLLM, DSPy, RouteLLM, Constitutional Classifiers). It also links commentary auditing TypeSafe's claims (accuracy vs. frontier LLM baselines, security issues found in community tools).
github.comrepoAdded 29 Sep 2026, published 17 Sep 2026🧠 AI - MichaelKinsy/PiG
PiG reimplements Pi — a minimal, extensible terminal coding agent — as a single native Go binary with no Node.js dependency, while remaining behaviorally pinned to a specific Pi release (0.87.1) and running Pi's TypeScript extensions unchanged. It adds a multi-language extension host (Go, Rust, Python, Node), a "Piglet" mechanism for bundling extensions/skills/prompts into a named shareable agent, and a formal parity-tracking process (PORT_MAP.md, DIVERGENCES.md, coverage reports) that documents every intentional divergence from the upstream Pi reference implementation.
github.comrepoAdded 27 Sep 2026, published 17 Sep 2026🧠 AI - crypt0p3g/adnullenum
adnullenum is a single-pass Active Directory enumerator that uses anonymous (null) SMB sessions over the \samr and \lsarpc named pipes to pull domain info, password/lockout policy, RID-cycled account inventory, per-user detail, and group membership without credentials. It consolidates what rpcclient, impacket's samrdump.py/lookupsid.py, enum4linux-ng, and NetExec each do separately into one run, falls back to LSA lookups when SAMR is locked down, flags interesting accounts (AS-REP-roastable, PASSWORD_NOT_REQUIRED, unconstrained delegation, etc.), and writes ready-to-use userlist.txt/computerlist.txt plus a reusable RID cache. The README also gives blue-team guidance on closing null-session access (RestrictAnonymousSAM, Pre-Windows 2000 Compatible Access group) and detecting it via Event 4661/4662/4624/5140.
github.comrepoAdded 2 Oct 2026, published 17 Sep 2026🛡️ Security - leepokai/jev-guard
jev-guard is an MIT-licensed hook layer that adds an auto mode to Claude Code, Codex, Copilot CLI, Gemini CLI, Cursor, pi, OpenCode, Antigravity and ACP editors. It asks the Jev model three typed questions (risk, user_requested, from_untrusted) per tool call and decides deny, ask or allow in about 20 lines of code. It also scans tool results for prompt injection and checks skills and plugins.
github.comrepoAdded 27 Oct 2026, published 17 Sep 2026🧠 AI - AnotiaWang/awesome-decision-models
A community-maintained GitHub list cataloging "decision models" (also called System One models): small/fast models that take a state plus caller-declared questions (Noul/true-false, Choice/multi-option, Score/rubric) and return a probability per answer in one forward pass, rather than generating text. It tracks the originating TypeSafe AI Jev model and its /v1/systemone API alongside competing hosted models (Upstage Solar Decide, Liquid AI's d1, OpenAI's Decisions API, Inception's Mercury Decide, Respan's Span-01), dozens of open-weight fine-tunes (Cloudflare's Clef, Perplexity's pplx-decider, AWS Strands Decider, Together AI's Tev1, and many Qwen3.5-based community models), zero-training logit-reading approaches, local runtimes (Ollama, Ollaya, llama.cpp-based servers), SDKs across a dozen languages, and a very long list of agent/coding-tool/MCP integrations (browser agents, code review, routing, game-playing demos) that use these models for fast, typed, in-the-loop decisions. The page is truncated at 40k of ~51k characters, so later sections (further toys, demos, and possibly benchmarks) are not reflected here.
github.comrepoAdded 2 Oct 2026, published 17 Sep 2026🧠 AI - Dicklesworthstone/skillranker
SkillRanker (sr) is a standalone Rust CLI that ranks which skill an agent should load next, combining local context/roster signals with TypeSafe.ai's Jev model for evaluation and FrankenSearch's Quill BM25 engine for local candidate prefiltering when a skill library exceeds 254 entries. It integrates with Claude Code and Codex via hooks, offers dry-run/explain/replay/eval workflows for inspecting and reproducing ranking decisions, and is explicitly advisory only — it never executes skills or overrides agent instructions.
github.comrepoAdded 26 Sep 2026, published 17 Sep 2026🧠 AI - Copy Fail (CVE-2026-31431): 9-year-old Linux kernel LPE found by Theori's Xint Code
A GitHub repository from Theori's Xint Code team detailing CVE-2026-31431, a Linux kernel local privilege escalation bug ("Copy Fail") that had gone undetected for roughly nine years. The researchers confirmed exploitability across current production kernels including Ubuntu 24.04 LTS (6.17.0-1007-aws), Amazon Linux 2023 (6.18.8-9.213.amzn2023), RHEL 10.1 (6.12.0-124.45.1.el10_1), and SUSE 16 (6.12.0-160000.9-default).
github.comrepoAdded 17 Sep 2026🛡️ Security - NiazMorshed2007/jev-review
Jev Review is a local MCP server that gives coding agents structured per-dimension quality scores on diffs or files, using a remote Jev API for scoring. It supports an iterative loop where agents baseline, improve, and rescore code with delta comparisons.
github.comrepoAdded 26 Sep 2026, published 17 Sep 2026🧠 AI - ThreatIntel-Aggregator
ThreatIntel-Aggregator is a self-hosted FastAPI/Next.js platform that polls 60+ tiered security RSS feeds (CISA, Talos, Unit42, etc.), runs AI triage to score severity and tag MITRE ATT&CK TTPs, extracts IOCs/CVEs, and correlates findings against a RunZero asset inventory to surface org-level exposure. Its Detections module goes further: it catalogs AI-generated or locally-imported detection rules (KQL/Sigma/YARA/Suricata/SPL), statically validates them, runs AI-driven MITRE alignment checks against technique coverage, tracks detection "rot," and can sync Hunts/Analytics Rules to a live Microsoft Sentinel workspace. It's designed to run standalone with zero cloud dependency or fully integrated with Azure/Entra/Sentinel, with all storage in Postgres and auth via Entra SSO or a local API key.
github.comrepoAdded 22 Sep 2026, published 17 Sep 2026🛡️ Security - All-AI-Jailbreaks
A GitHub repository archiving 19 jailbreak, prompt-injection, persona-conditioning, and response-format-manipulation prompts collected against DeepSeek, Gemini, GLM, Grok, Kimi, Qwen, Sonnet, and ChatGPT. Prompts are kept close to their original form for provenance/reproducibility, positioned as a corpus for red-teaming and robustness evaluation rather than a guaranteed exploit list, with guidance to test in isolated environments and log model version/config/date/response per trial.
github.comrepoAdded 22 Sep 2026, published 17 Sep 2026🛡️ Security - AI Agent Hacking Writeups
A GitHub-hosted, CC0-licensed index of 281 public writeups on attacks against AI agents, organized into six categories: indirect prompt injection, direct prompt injection/jailbreaks/guardrail bypass, MCP and agent tooling, AI platform/infrastructure bugs, classic web bugs in AI product surfaces, and AI used as an attacker's tool. Entries span 2021-2026 and include major disclosures like GeminiJack, ForcedLeak, Clinejection, CVE-2025-53773 (GitHub Copilot RCE), and dozens of Johann Rehberger/PromptArmor/qual1a writeups covering exfiltration, MCP OAuth flaws, and coding-agent sandbox escapes. Comes with an accompanying blog post "How to Hack AI Agents" and a scripted links.txt for automation.
github.comrepoAdded 22 Sep 2026, published 17 Sep 2026🛡️ Security - Markakd/Container_escape
A GitHub repository hosting target-specific proof-of-concept exploits for two Linux kernel vulnerabilities, CVE-2026-52910 and CVE-2026-80521 (the latter an AF_UNIX kernel bug also documented in a kernelCTF LTS exploit-chain submission), both usable to break out of container isolation. The project ships a QEMU/Docker-based disposable VM builder (pinned to specific Ubuntu cloud images and kernel versions) so the destructive PoCs can be compiled and detonated only inside throwaway guests rather than on real hosts.
github.comrepoAdded 2 Oct 2026, published 16 Sep 2026🛡️ Security - Shai-Hulud-2.0-Detector — npm supply-chain compromise scanner
Shai-Hulud-2.0-Detector is a GitHub Action and CLI tool that scans package.json/lockfiles for packages compromised in the Shai-Hulud 2.0 (Nov 2025) and ChainDrop (Aug 2026) npm supply-chain worms. It uses semver-precise matching against a database of 1,241+ known-compromised package versions (auto-updated daily from Datadog and Wiz Research feeds) to flag malicious preinstall/postinstall droppers (setup_bun.js, Math_Symbol.js), rogue GitHub self-hosted runners named SHA1HULUD, and ChainDrop's new IDE-persistence hooks in .claude/settings.json and .vscode/tasks.json. It ships SARIF output for GitHub Security tab integration, an allowlist system, and a detailed incident-response guide covering credential rotation and forensic checks.
github.comrepoAdded 16 Sep 2026🛡️ Security - Mapika/decider
Decider is an open reproduction of TypeSafe AI's System One (Jev) model class: instead of generating text, it reads a state plus a set of typed questions (Choice, Score, or Noul/yes-probability) and returns a calibrated probability distribution for each in one forward pass, with no decoding or parsing. The repo ships 2B/4B/12B and a 35B mixture-of-experts checkpoint (built on Qwen3.5 and Gemma-4 base models), trained on roughly 95 public datasets plus teacher-labelled data, with per-type temperature calibration, GGUF/llama.cpp and vLLM serving paths, an MPS/Apple Silicon port, and a community Snapdragon X Elite NPU port. It benchmarks against TypeSafe's Jev on JevBench and the Decision Index, documenting where it closes the gap (language, tools, retrieval) and where it lags (knowledge-heavy MMLU/GSM8K/GPQA tasks and calibration on hard items).
github.comrepoAdded 2 Oct 2026, published 16 Sep 2026🧠 AI - y0usaf/pi-jev
pi-jev is an npm extension (@y0usaf/pi-jev) that adds a typed decision layer to the Pi coding agent: a gate scores pending bash/write/edit tool calls on destructiveness, exfiltration risk, scope, and impact before they run, while an output judge scans bash results for leaked secrets and classifies command failures (retry/environment/code_bug/permission/user_error). Answers come back as probabilities or choice distributions rather than prose, are batched into one API round trip to api.typesafe.ai, cached per input, and fail open on any error so a dead endpoint never blocks the agent. The README documents calibration work behind the thresholds (e.g. destructive=0.90, leak=0.90) derived from repeated fixture runs, and details argument/output truncation and key redaction to limit what leaves the machine.
github.comrepoAdded 26 Sep 2026, published 16 Sep 2026🛡️ Security - y0usaf/pi-jev
pi-jev is a decision-layer extension for the Pi coding agent that asks a separate model (Jev/TypeSafe) typed yes/no, choice, or score questions about pending tool calls and their outputs, returning probabilities and confidence scores instead of prose. It gates bash/write/edit calls for destructive, exfiltration, and out-of-scope risk, judges bash output for leaked secrets and failure classification, and exposes a jev_ask tool for the model to request the same structured judgements itself. The README documents empirically calibrated thresholds (e.g. destructive=0.90, leak=0.90) derived from repeated test runs rather than arbitrary defaults.
github.comrepoAdded 26 Sep 2026, published 16 Sep 2026🧠 AI - bilibili/Index-Translate
Index-Translate is Bilibili's Apache-2.0 family of multilingual, multimodal translation models built on Qwen3.5 (2B, 9B and 35B-A3B preview), covering 150 languages with instruction following (glossaries, format preservation, tone). Variants add native image translation with no OCR (vision encoder), Index-Echo for speech subtitles and dubbing, Index-Homura for syllable-controlled translation and Index-NativeLong for full-document translation. The repo provides GGUF, FP8 and NVFP4 quantized builds, vLLM serving scripts, a free OpenAI-compatible API, four new benchmarks (instTrans, MEME, SandGlass, NAtIveLong), and links to three papers including HOMURA and RIVAL (RL for translation).
github.comrepoAdded 10 Oct 2026, published 15 Sep 2026🧠 AI - ruc-datalab/EvoOntology
EvoOntology is an open-source, self-evolving semantic ontology layer for data agents from Renmin University of China, exposed as MCP tools and installable as Claude Code and Codex plugins. It automatically builds a versioned ontology from tabular/file/database workloads, then continuously evolves it from agent execution trajectories using a build-use-evolve-evaluate-publish loop that validates candidate updates against a parent version before promotion. The accompanying paper reports gains over plain ReAct agents on DDR-Bench, InsightBench, and BIRD across GPT-5.5, GPT-5.6-sol, Claude-Sonnet-5, and Claude-Opus-4.8 backbones.
github.comrepoAdded 26 Sep 2026, published 15 Sep 2026🧠 AI - Cloudflare security-audit-skill
security-audit-skill is a Cloudflare open-source coding-agent skill that turns an AI coding agent into a structured vulnerability hunter, running six phases: reconnaissance into architecture.md/coverage-ledger.json, coverage-led hunting by isolated sub-agent "hunters," adversarial candidate validation, structured findings.json output validated against a report-schema.json, independent re-verification of claims, and target-neutral report generation (REPORT.md, FINDINGS-DETAIL.md, NEEDS-VALIDATION.md). It is installed via the Skills CLI (`npx skills add`), uses Node.js validators (validate-coverage-ledger.cjs, validate-findings.cjs), requires a sandboxed environment for safely executing target code/tests/fuzzers, and is the single-repo seed for Cloudflare's larger fleet-wide vulnerability discovery harness described in a companion blog post.
github.comrepoAdded 22 Sep 2026, published 15 Sep 2026🛡️ Security - OpenHunterAI
OpenHunterAI is a self-hosted, alpha-stage AI red-teaming workspace that applies attacker-style reasoning to web, API, and LLM application security testing against verified, in-scope public targets. It runs locally via Docker/Node.js, orchestrates bounded testing (scope lock → surface mapping → baseline → hypothesis testing → evidence gating → report/retest) through Go workers over NATS, and ships adapters for browser inspection, OWASP ZAP, and Nuclei, with separate OpenHack and Strix runtime integrations and an agent skill for Claude Code/Codex/Gemini CLI/Grok.
github.comrepoAdded 22 Sep 2026, published 15 Sep 2026🛡️ Security - Maskit
Maskit is a local privacy gateway that sits between AI coding tools (Cursor, Claude Code, Codex, ChatGPT, Claude, DeepSeek) and the model provider, automatically redacting sensitive data — API keys, database connection strings, private IPs, PEM keys, JWTs, PII like phone numbers/ID numbers — into placeholders before requests leave the machine, then streams responses back with the placeholders transparently restored. It works as a local reverse proxy (per-protocol ports for OpenAI/Anthropic/DeepSeek) plus a browser extension (Chrome/Edge MV3) that intercepts Fetch/XHR traffic on ChatGPT, Claude and DeepSeek web UIs, including redaction of uploaded Office documents. It also includes a lightweight local ONNX NER model for names/orgs/addresses, placeholder consistency across multi-turn conversations, and passive prompt-injection detection on model replies.
github.comrepoAdded 22 Sep 2026, published 15 Sep 2026🛡️ Security - WordPress Security Skills
WordPress-Security-Skills is a GitHub repo of modular 'Agent Skills' (per the open Agent Skills spec) that install into AI coding agents like Claude Code, Cursor, Codex, OpenCode, and Gemini CLI to guide secure-by-default WordPress plugin/theme development and security code review. Each skill targets a documented failure mode in AI-generated WordPress code — missing nonce checks, broken authorization, missing output escaping, unprepared SQL queries — with when-to-use guidance, common AI mistakes (wrong vs right), code examples, and checklists tied to official WordPress API references. It is explicitly instructional Markdown/PHP reference material, not a scanner or automatic protection, meant for developers and reviewers auditing AI-written or third-party WordPress code.
github.comrepoAdded 22 Sep 2026, published 15 Sep 2026🛡️ Security - MassPIIFinder v2
MassPIIFinder v2 is a Python recon tool that automates crawling a target's in-scope JavaScript (multi-hop HTML crawl, dynamic imports, chunk manifests, sourcemaps, plus optional passive CT-log subdomain discovery) and mines it for API keys, tokens, credentials, internal endpoints, and PII using ~90 named patterns plus a high-entropy freeform heuristic. Findings are validated offline (Luhn checks, JWT decode, AWS key-shape) and via scope-checked, rate-limited reachability probes, then triaged by severity and exported as JSON/HTML/SARIF/Markdown/CSV. It enforces authorization with a required --confirm-authorized flag and a ScopeGuard that blocks any out-of-scope requests, and explicitly avoids testing leaked keys against third-party providers or exploiting findings.
github.comrepoAdded 22 Sep 2026, published 15 Sep 2026🛡️ Security - KillaBoi/BrokenPipe
BrokenPipe is a PowerShell PoC that escalates a standard Windows user to NT AUTHORITY\SYSTEM by abusing the Steam Client Service (steamservice.exe). It connects to the service's shared-memory IPC, whitelists a genuine Valve-signed install-script VDF against a caller-controlled installation root (IClientInstallUtils::AddInstallScriptToWhiteList), then triggers RunInstallScript so the SYSTEM service launches a relocated executable (by default cmd.exe) without any UAC prompt. The flaw was reported to Valve in March and remained unpatched as of the write-up, validated on Steam 10.96.30.42 on Windows 10/11 x64.
github.comrepoAdded 2 Oct 2026, published 14 Sep 2026🛡️ Security - DeathShotXD/0xCr0ssCrush
Research project on two signed vulnerable Windows drivers, DCRCVDrv.sys (MOCOMSYS) and Alinubx.sys (CnCrypt), abused by the Cruciferra MaaS loader to kill AV/EDR processes. It documents their devices, IOCTLs (0x2205C0, 0x222024) and the termination chain (ObOpenObjectByPointer -> ZwTerminateProcess), and gives annotated disassembly, hash-level sample provenance and blocklist-status snapshots. It includes a Rust lab harness with hash validation and dry-run, plus Sigma, YARA and telemetry guidance. Findings carry evidence labels, and the test matrix is limited to Windows 11 24H2 with HVCI disabled.
github.comrepoAdded 11 Oct 2026, published 14 Sep 2026🛡️ Security - bsab/sweden-mcp-servers
A community-maintained catalog of Model Context Protocol servers connecting AI assistants to Swedish data, laws and services (e.g. Fortnox, Bokio, BolagsAPI, ICA), forked/adapted from the France and Italia MCP Servers projects. Each entry is checked against canonical documentation, tracks license/credential requirements, and includes a runtime smoke-test report (protocol/tool call attempts, credential blockers, failures) plus a six-criterion documentation-readiness rubric, published as a static JSON/HTML site.
github.comrepoAdded 26 Sep 2026, published 14 Sep 2026🧠 AI - Pal-AI-Lab/Cortico
Cortico is an open-source agent harness built around an event stream, designed for autonomous, continuously running agents that handle mixed real-time input across chat platforms, live games, and even physical environments. It provides modular LLM provider components (via an internal Responses protocol), unconstrained context/memory management, an isolated extension system called Cortico World, and a WebUI, with a companion AI-assisted extension creator (Cortina) that lets non-developers build extensions through conversation. A reference use case is cortico-world-vtuber, which drives a Live2D model via VTube Studio with streaming TTS and OBS overlay integration.
github.comrepoAdded 26 Sep 2026, published 13 Sep 2026🧠 AI - RepoGuardBench
RepoGuardBench is a benchmark and accompanying paper that measures whether local open-weight coding agents (Qwen2.5-Coder 1.5B-14B via Ollama) stay on the bug-fix task when repository artifacts — README files, issue text, code comments, test logs, and agent-rule files — carry inert prompt-injection instructions. It evaluates five lightweight context- and action-level defenses (D0-D5, including a path-only action gate) across seven metrics in a sandboxed task workspace, finding no statistically clear utility winner among them. The project ships a deterministic no-GPU smoke test, paper-claim verification scripts, and reproducible tables/figures under MIT (code) and CC BY 4.0 (data) licenses.
github.comrepoAdded 22 Sep 2026, published 13 Sep 2026🛡️ Security - shinthink/blitzstrike
Blitz Strike is an open-source Model Context Protocol server (TypeScript/Bun) that packages a structured 3-tier pentesting methodology — BLITZ (attack-surface recon), EAGLE-EYE (source-to-sink reachability tracing), and STRIKE (live validation before reporting) — into callable tools any MCP client (Claude Code, Cursor, Gemini, etc.) can drive with a single run_engagement call. It ships 130 self-written security tools, 317 indexed tool manuals, 58 data-driven escalation chains with negative-control checks, a Web3/Solidity audit module with Foundry proofs, and a regression/benchmark suite (453 checks, reported 1.0 detection / 0 false-positive rate) to make every finding verified rather than pattern-matched.
github.comrepoAdded 2 Oct 2026, published 12 Sep 2026🛡️ Security - agent-egress-bench
Agent Egress Bench is an open, tool-neutral benchmark maintained by PipeLab (makers of Pipelock) that tests whether products mediating an AI agent's outbound traffic — proxies, egress firewalls, MCP wrappers, agent gateways — actually catch exfiltration attempts caused by prompt injection or misalignment, rather than testing the underlying model itself (that's left to AgentDojo, InjecAgent, CyberSecEval, AgentHarm, ASB). It ships a reproducible Go runner with a proxy/WebSocket/MCP/A2A adapter contract, an offline validator, DSSE-signed evidence bundles, and a CI-runnable GitHub Action, and separates containment from false-positive rate as two distinct scored axes with immutable case IDs and OWASP Agentic Top 10/MITRE ATT&CK mappings. Its governance explicitly permits third parties to publish results unfavorable to the maintainer's own Pipelock product.
github.comrepoAdded 12 Sep 2026🛡️ Security - CassiopeiaCode/CosyRedactGateway
Cosy (CosyRedactGateway) is a Node.js gateway that sits between programmers' LLM clients and OpenAI or Anthropic APIs. It replaces credentials found in JSON request text with reversible SHA-256-based placeholders, using high-entropy scoring, structured detectors and Gitleaks-compatible rules, and restores them in responses, SSE streams and tool arguments. It runs on Cloudflare Workers, Deno or locally, and documents its limits: auth headers are still forwarded, and misses are possible.
github.comrepoAdded 19 Oct 2026, published 11 Sep 2026🛡️ Security - CassiopeiaCode/CosyRedactGateway
Cosy (CosyRedactGateway) is a local-first LLM credential redaction gateway. It replaces secrets in request JSON with reversible SHA-256 placeholders before forwarding to OpenAI or Anthropic upstreams, then restores them in responses, SSE streams and tool-call arguments. Detectors cover high-entropy strings, structured patterns and Gitleaks-compatible rules. It runs on Node.js, Cloudflare Workers or Deno, with an offline demo script and a documented list of limits.
github.comrepoAdded 19 Oct 2026, published 11 Sep 2026🧠 AI - CVE-2026-42533 nginx heap buffer overflow PoC (pre-auth RCE via two-pass capture clobbering)
A public PoC repo for CVE-2026-42533, a pre-auth heap buffer overflow in nginx's two-pass string evaluation engine that occurs when a regex-based map directive using numbered captures ($1, $2) clobbers the shared r->captures state used by a regex location, causing a LEN/VALUE size mismatch. The overflow can corrupt an adjacent ngx_pool_cleanup_t structure to hijack a function pointer for RCE, or under-write to leak heap/libc pointers defeating ASLR; the repo ships exploit.py/leak.py/overflow.py plus a Docker test environment demonstrated at 10/10 reliability on Ubuntu 24.04 against nginx 0.9.6-1.30.3/1.31.2. It also documents the exact vulnerable config pattern, a config scanner link, and the fix (named captures or upgrade to nginx 1.30.4+/1.31.3+).
github.comrepoAdded 10 Sep 2026🛡️ Security - sage — Agent Detection & Response (ADR) for AI coding agents
Sage is an "Agent Detection & Response" (ADR) security layer that intercepts tool calls made by AI coding agents — shell commands, URL fetches, file writes — and screens them through multiple detection layers before execution. It combines cloud URL reputation, 300+ YAML local heuristics, a two-tier (heuristic + fine-tuned ML) prompt-injection detector for fetched content, npm/PyPI package supply-chain checks (registry existence, file reputation, age), installed-plugin scanning at session start, and Windows AMSI integration. It ships as a plugin for Claude Code, Cursor, VS Code, OpenClaw, and OpenCode, and is published by Gen Digital (also distributed under the Norton/Avast Sage branding).
github.comrepoAdded 10 Sep 2026🛡️ Security - AWSHound — AWS BloodHound OpenGraph Collector
AWSHound is a Go CLI/container tool that collects AWS IAM and authorization data across profiles, config-file opt-ins, or an entire AWS Organization (via cross-account role assumption), and outputs a BloodHound OpenGraph for attack-path analysis. It supports phased collection with on-disk artifacts, offline graph building from previously collected data, and safeguards like --max-api-requests and --max-api-requests-per-minute to bound AWS API traffic during collection.
github.comrepoAdded 8 Sep 2026🛡️ Security - GhostJS
GhostJS is an open-source Burp Suite extension by TrinetLayer that passively scans JavaScript, HTML, and JSON responses flowing through Burp for hardcoded secrets (AWS/GCP/Azure keys, Stripe/PayPal/GitHub tokens, JWTs, private keys, etc.) and hidden API endpoints, surfacing findings in a dedicated tab with severity, confidence scoring, remediation guidance, and Markdown export. It also actively fetches referenced <script> bundles using the tester's live session cookies and applies a false-positive filter to suppress doc-sample and placeholder keys, making it a practical recon aid during authorized web app pentests and bug bounty work.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - vet (SafeDep)
vet is an open-source CLI (from SafeDep) that scans package manifests, SBOMs, container images, and source repos across npm, PyPI, Maven, Go, RubyGems, Cargo, and Packagist to surface vulnerabilities, malicious packages, and license/quality issues. It cuts through CVE noise by analyzing actual code-usage evidence, queries SafeDep Cloud's threat-intelligence database for real-time malware detection (e.g. flagged packages like express-cookie-parser, eslint-config-airbnb-compat), and lets teams enforce security/license/OpenSSF-Scorecard policies as CEL expressions in CI/CD via SARIF/JSON/Markdown reporting.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - headroomlabs-ai/headroom
Headroom is an open-source (Apache 2.0) local compression layer that sits between AI agents and LLM providers, compressing tool outputs, logs, RAG chunks, files and conversation history before they reach the model. It offers a Python/TypeScript library, a drop-in proxy, an `headroom wrap` mode for popular coding agents (Claude Code, Codex, Cursor, Copilot, Aider, etc.), an MCP server, cross-agent shared memory with dedup, and output-token reduction via verbosity steering and effort routing — all running locally with reversible compression (CCR) so originals stay retrievable.
github.comrepoAdded 23 Sep 2026, published 7 Sep 2026🧠 AI - pashov/skills
pashov/skills is a set of Claude Code "skills" built by Pashov Audit Group that turn an AI coding agent into a Solidity security auditor: an "x-ray" command for quick codebase reconnaissance, a "solidity auditor" mode that runs multiple different agent personas over a codebase (or specified files) looking for vulnerabilities, and a "fizz" command for additional automated checks. It packages smart-contract audit tradecraft into reusable AI agent skills rather than a standalone scanner, letting developers or auditors invoke deep, multi-pass Solidity review directly inside their coding assistant.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - PlamenTSV/plamen
Plamen is an open-source Python orchestrator that drives 18-100 Claude Code or OpenAI Codex CLI agents across 40+ phases to autonomously audit smart contracts (EVM/Solidity, Solana/Anchor, Aptos Move, Sui Move, Soroban, DAML/Canton) and L1 node-client infrastructure (Go/Rust consensus, p2p, mempool code), producing a severity-tiered AUDIT_REPORT.md with verified proof-of-concept exploits for each finding. It integrates MCP servers for Slither, ChromaDB and Solodit, ingests vulnerability corpora from Solodit, DeFiHackLabs and Immunefi to ground findings, and runs a PTY-supervised worker-pool architecture with checkpoint/resume, artifact-based completion gating, and a dedicated L1 mode with consensus-invariant and network-surface depth agents.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - trailofbits/skills
Trail of Bits maintains a Claude Code plugin marketplace of "skills" that extend AI coding agents (Claude Code, Codex, ChatGPT workspaces) with security analysis, testing, and secure development capabilities. It's installed via `/plugin marketplace add trailofbits/skills` and is also compatible with Codex's Claude marketplace support, with related sibling repos for curated skills, devcontainers, and config.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - bikini/exploitarium
Exploitarium is a consolidated GitHub archive of an independent researcher's proof-of-concept vulnerability writeups, merging over a dozen former standalone PoC repos into one. It covers diverse real-world targets including RustDesk session permission bugs, an OpenSSH agent lock provider bypass, a Redis VSET duplicate HNSW ID RCE, a QEMU CXL Type3 mailbox escape, Firefox native/backup NSS RCE PoCs, libssh2 CVE-2026-55200, Nextcloud federated share bearer token issues, and more. The author documents an AI-assisted fuzzing workflow (hand-typed PoCs, AI-drafted READMEs) and credits prior work on an objdump OOB write finding.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - 0x4D31/endpoint-ai-agent-abuse
endpoint-ai-agent-abuse (EAA) is a curated, evidence-scoped taxonomy of techniques for abusing local, endpoint-resident AI agents — especially coding and developer agents — covering launchers/flags, provider routing, instructions, memory, hooks, plugins, skills, MCP, transcripts, telemetry, and inherited local-user authority. Each technique is tagged by maturity (feasible, demonstrated, observed) and backed by cited incidents, artifacts, or research, with companion files for surfaces, tactics, case mappings, and detection/hunting hypotheses plus a validator script and JSON schema for the catalog.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - mukul975/cve-mcp-server
cve-mcp-server is a Model Context Protocol server that gives Claude direct access to 28 security tools spanning 24 APIs (NVD, EPSS, CISA KEV, OSV.dev, GitHub GHSA, MITRE ATT&CK, AbuseIPDB, GreyNoise, Shodan, VirusTotal, MalwareBazaar, ThreatFox, Ransomwhere, and more), fronted by a one-call triage_cve orchestrator. It computes a composite 0-100 risk score from CVSS, EPSS, KEV status, and PoC availability (with a hard CISA KEV override forcing CRITICAL/≥76), supports dependency scanning via OSV, IP/domain reputation lookups with private-IP blocking, and ships an SSVC v2 gated decision mode plus audit logging and XML-bomb protections via defusedxml.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - andyrewlee/awesome-agent-orchestrators
A curated GitHub list cataloguing open-source and source-available tools for orchestrating AI coding agents, organized into categories: terminal multiplexers/TUIs (tmux+worktree managers like claude-squad, amux, agent-manager), desktop/web parallel-session apps (Ghostex, Tempest, Vicoa), multi-agent swarms with inter-agent coordination (crewAI, gastown, loki-mode), autonomous loop runners (Ralph Wiggum-style loops like ralph-orchestrator, bernstein), issue/board-driven task runners (cyrus, open-swe, claude-code-action), infrastructure/control-plane primitives (Concord MCP, Agent Messaging Protocol), and always-on personal assistants (openclaw, rowboat). It covers dozens of tools working with Claude Code, Codex, Gemini CLI, OpenCode, and other agent CLIs, plus a watchlist of stalled projects. Useful as a map of the fast-moving agent-orchestration tooling landscape as of mid-2026.
github.comrepoAdded 23 Sep 2026, published 7 Sep 2026🧠 AI - kaandemir993/DarkTortilla-RAT-Telegram-Exfiltration-Payload-Extraction-Analysis
A hands-on reverse-engineering writeup dissecting a DarkTortilla RAT sample (pulled from MalwareBazaar) using Process Hacker, Binary Ninja and x64dbg. It documents the malware's credit-card theft (card_number_encrypted strings for Visa, Mastercard, Amex, Diners Club, etc.), browser credential theft via SQLite queries against Login Data files and app_bound_encrypted_key/os_crypt decryption, and three parallel exfiltration channels — a Telegram bot, SMTP mail, and FTP upload — with the C2 domain showip.net used for IP detection.
github.comrepoAdded 30 Sep 2026, published 5 Sep 2026🛡️ Security - ForgeGuardian
ForgeGuardian is an open-source (Apache 2.0) supply chain security scanner covering 9 package ecosystems (npm, PyPI, Go, Maven, RubyGems, Cargo, NuGet, Hugging Face, GitHub Actions) via 8 concurrent scan engines and 223+ built-in malicious-package detection signatures. It runs fully offline/local-first, offers a CLI (fgctl) and self-hosted SOC-style dashboard, generates CycloneDX/SPDX SBOMs, supports Sigstore keyless signing and provenance tracking, policy-as-code rules, dependency topology/attack-surface mapping, drift detection with auto-quarantine, and SARIF output for GitHub Actions CI integration, plus optional AI-powered advisory/patch-agent triage.
github.comrepoPublished and added 5 Sep 2026🛡️ Security - The React Native Developer's Security Guide
A GitHub-hosted book focused entirely on securing the React Native developer's workstation and toolchain rather than the shipped app — covering the polyglot execution surface triggered by a single git clone/yarn/pod install (Ruby, CocoaPods, Xcode build phases/XCSSET, Gradle, gradle-wrapper.jar, keystores), CVE-2025-11953 (exposed Metro/RN dev server), ClickFix-style social engineering of developers, CI-as-extended-workstation risks, and Expo/EAS-specific supply-chain concerns. It ships alongside a separate companion repo of 119 Opengrep detection rules, each mapped to a specific chapter's attack technique, plus practical appendices like a safe-clone runbook and a file risk atlas for hardening teams.
github.comrepoPublished and added 5 Sep 2026🛡️ Security - OWASP OASIS
OWASP OASIS is a proposed community project that operationalizes turning automated vulnerability/fix-generation tool output into human-validated pull requests submitted upstream to open source projects. It defines a full lifecycle (intake, weighted validator review with accept/reject/modify/duplicate decisions, OWASP adoption, ephemeral working forks, upstream submission) plus roles (project owners, validators, maintainer liaisons, automation operators) and outcome metrics like upstream acceptance rate. The GitHub repo lays out governance via a validators.yml credibility file, CODEOWNERS-gated scoring, and GitHub Projects/issue templates to run the whole thing without custom tooling.
github.comrepoPublished and added 5 Sep 2026🛡️ Security - Numbat
Numbat is a Go-based, single-binary endpoint agent from Perplexity AI that gives visibility into AI coding-agent activity (Claude Code, Codex, OpenClaw, and other CLI/IDE/gateway agents) by capturing events through local hooks, OTLP/HTTP logs, and on-disk session artifacts. It normalizes activity into one event model, evaluates it with a local CEL rule engine (including multi-step sequence rules like secret-read-then-egress), and can optionally block matched actions via synchronous pre-action hooks (deny/monitor decisions), with case bundles and SHA-256 manifests for forensic reconstruction. Example built-in rules detect cloud-metadata SSRF requests (169.254.169.254) and credential-exfiltration chains, mapped to MITRE ATT&CK technique tags.
github.comrepoPublished and added 5 Sep 2026🛡️ Security - iamzulx/crypto-rag
crypto-rag is an Indonesian-language CLI crypto assistant that pairs a static knowledge-base RAG pipeline with live market data tool calls, built on the principle that volatile numbers (price, funding rate, TVL, sentiment) must never be embedded in the vector store since they go stale instantly. It implements hybrid retrieval (BM25 keyword search + FAISS dense embeddings fused via Reciprocal Rank Fusion) over a 146-topic knowledge corpus, an optional cross-encoder reranker, and an intent router that dispatches price/derivatives/on-chain/sentiment queries to live sources (Binance, DefiLlama, Fear & Greed Index) versus concept questions to the corpus. A tool-calling agent handles multi-step queries, and an OpenAI-compatible LLM synthesis layer (works with StepFun, OpenAI, Groq, LM Studio, Ollama) grounds answers with citations and falls back to extractive answers when no LLM is configured.
github.comrepoAdded 2 Oct 2026, published 5 Sep 2026🧠 AI - eldarshiraliyev/BugScanner
BugScanner is an asyncio/httpx Python framework for recon and automated web vulnerability scanning, with a React and FastAPI dashboard. It covers subdomain enumeration (crt.sh, DNS brute force), TCP port scanning, fingerprinting, and modules for XSS, SQLi, CORS, SSRF, open redirect, JWT, IDOR and business logic, plus a Nuclei wrapper. A 5-rule false-positive filter with SPA detection, adaptive rate limiting, WAF detection and SARIF export are included.
github.comrepoAdded 20 Oct 2026, published 5 Sep 2026🛡️ Security - kajisho5/ffmpeg-skill
ffmpeg-skill is an Agent Skill (SKILL.md plus 42 stdlib-only Python tools) that lets Claude Code, Cursor, Codex and other agents edit video and audio with local ffmpeg/ffprobe. It enforces a probe → edit losslessly → check → verify workflow, and every tool takes --dry-run, --json and --plan. A machine-readable contract, whose input schemas are derived at run time from each script's argparse parser (the author's "SPEC" pattern), drives an MCP server that lists a core 12 tools by default. The repo also ships per-platform render templates, a doctor capability check, a test suite and evals. It is useful as a worked example of a deterministic, verifiable skill/tool layer in which the agent supplies judgement and the tools do the work.
github.comrepoAdded 16 Oct 2026, published 3 Sep 2026🧠 AI - N4darae/shrt
shrt is a Go command-line tool for regression testing RPC backends. Agents, such as Claude Code through a SKILL.md skill, write per-domain contract overlays, and the planner composes RPC chains that probe boundaries, other roles, missing tokens and read-backs after writes. The tool runs and verifies chains against approved runs, and a gate command checks every new release. A person must approve any chain before it becomes a baseline.
github.comrepoAdded 23 Oct 2026, published 3 Sep 2026🧠 AI - h5i-dev/awesome-ai-agent-incidents
A curated GitHub corpus tracking real-world security incidents, CVEs, attack techniques, and defensive tools specific to autonomous AI agents — spanning prompt injection/goal hijacking, MCP client-side tool-metadata poisoning, the "Promptware Kill Chain" multi-stage attack model, MITRE ATLAS agentic techniques, and the OWASP Top 10 for Agentic Applications. It also documents the OpenClaw/ClawHub supply-chain incident (1,184 malicious skills confirmed by Antiy CERT) and links defensive projects like OWASP Agent Memory Guard for LangChain/LlamaIndex agent memory protection.
github.comrepoAdded 3 Sep 2026🛡️ Security - Agenta-AI/awesome-ai-agent-platforms
A curated, CC0-licensed GitHub list cataloguing open-source AI agent platforms across five categories: persistent AI coworkers (Agent Zero, Agenta, LibreChat, LobeChat, Open WebUI, OpenClaw), developer agent frameworks (CrewAI, LangGraph, LlamaIndex, Haystack, Langflow, Letta, Agno, Pydantic AI, OpenAI Agents SDK), workflow/automation runtimes (n8n, Temporal, Prefect, Dagster, Apache Airflow, Windmill), browser agents (Browser Use, Skyvern), and coding agents (Aider, Cline, Goose, OpenHands, Open Interpreter). Each entry states a factual one-line description plus its license and hosting model, with selection criteria requiring an active repo, a usable product, and verifiable licensing — companion comparison table hosted at aiagentplatforms.dev.
github.comrepoAdded 30 Sep 2026, published 2 Sep 2026🧠 AI - ProjectDXAI/continuous-record-llm-trading-agents
Companion repository for the DXRG paper "What LLM Trading Agents Actually Do in Production" (arXiv:2609.05663), reporting a six-month, population-scale record of two live LLM-agent trading fleets: 3,505 DX Terminal Pro vaults on Base and a 500-599 agent DXAP fleet on Hyperliquid perpetuals (231,638 finalized turns, 14,596 fills). It quantifies how the operating layer — not strategy text — drives behavior: a prompt-rendered leaderboard routes 46.5% of trade entries with a sharp regression discontinuity at the render boundary, agent fixed effects absorb 60% of outcome variance, leverage choice is volatility-blind (median 5.0x across a 5.7x volatility spread) with one posture/slider cell concentrating 62% of liquidations, and discretionary exits underperform a fixed 2%/4% bracket. A 416-scenario paired replay across three frontier models found similar decision quality but sharply different choice-consistency flip rates (35% vs 90%+), and the repo ships the paper, figures, aggregate data extracts, dataset cards and a 17-rule methodology canon distilled from the project's own retracted claims.
github.comrepoAdded 2 Oct 2026, published 1 Sep 2026🧠 AI - cyanheads/osv-advisory-mcp-server
osv-advisory-mcp-server is an MCP server that queries the OSV.dev vulnerability database, offering single-package version checks, batch audits of up to 1000 {name, ecosystem, version} tuples for SBOM/lockfile triage, and full advisory record fetch by OSV ID (GHSA/PYSEC/RUSTSEC/GO/DSA/DLA/CVE prefixes). It surfaces CVE aliases, CVSS vectors, derived severity labels, and CWE IDs, and is designed to chain into a companion nist-nvd-mcp-server for CVSS base scores, EPSS probability, and CISA KEV status. It ships as a keyless, no-API-key tool runnable via STDIO or Streamable HTTP, with a public hosted instance and Bun/npx/Docker install paths.
github.comrepoAdded 1 Sep 2026🛡️ Security - Nehanth/pooled
Pooled runs one open model (Qwen 3.6 35B MoE, a 27B dense hybrid, smaller Qwen3/SmolLM) across devices in a browser "room". Each tab holds a slice of layers and runs them on its own GPU with custom WGSL kernels. Hidden states pass over WebRTC, and speculative decoding is checked against plain decoding by golden tests. It also ships a Code-mode agent loop with a sandboxed preview, and an npx CLI bridge (@pooled/cli) that exposes the room as an OpenAI Chat Completions/Responses and Anthropic Messages endpoint with grammar-constrained tool calling, so Codex CLI, Claude Code and opencode can use it. The README includes latency-injected benchmarks, a comparison with exo, Petals, llama.cpp RPC and WebLLM, and a threat model.
github.comrepoAdded 16 Oct 2026, published 1 Sep 2026🧠 AI - rollroyces/py-idp
py-idp is a Python framework for intelligent document processing with a six-stage pipeline (parse, classify, extract, assess, validate, human review). It supports 23 LLM backends including OpenAI, Anthropic, Ollama, and self-hosted Nanonets-OCR2-3B. It adds Pydantic schema extraction, auto-chunking of oversized documents, an eval harness, and a review-driven policy update for confidence. It is dual-licensed AGPL-3.0 and commercial.
github.comrepoAdded 23 Oct 2026, published 31 Aug 2026🧠 AI - PackageGuard
PackageGuard is an open-source .NET CLI tool that scans NuGet, npm, pnpm and Yarn dependencies (direct and transitive) across a codebase, enforcing hierarchically-configured allow- and deny-lists for licenses, packages and versions. It scores each package's Legal, Security and Operational risk using signals like OSV vulnerability data, maintainer activity, package signing and release cadence, and can emit a CycloneDX or SPDX SBOM enriched with OSV vulnerability data, plus console, HTML and SARIF output for CI/GitHub code scanning. It's positioned as a free alternative to commercial supply-chain tools like Black Duck and Snyk.
github.comrepoPublished and added 31 Aug 2026🛡️ Security - galyarder-security
galyarder-security (formerly Shannon Proxy) is a Docker/Temporal-based auditing layer that intercepts model SDK calls (Anthropic, Groq, local Ollama, etc.) and routes them through a local proxy on port 8317 rather than direct cloud endpoints, giving operators visibility into and control over what autonomous coding/tool-using agents execute. It runs structured "security sweep" and threat-modeling workflows against a target repo (`./shannon start`) and includes deterministic cleanup routines (`./shannon cleanup`) to remove agent-generated scripts and execution residue and prevent workspace pollution/exposure. It targets a threat model broader than chat-based prompt injection: agent tool-execution drift, dependency supply-chain issues, and unverified code paths in "agentic company" shell-access workflows.
github.comrepoPublished and added 31 Aug 2026🛡️ Security - choirboy-prompt
choirboy-prompt is a cross-runtime agent-memory plugin that loads project lore, research indexes, and validated dossiers into agent sessions via SessionStart hooks (Claude Code, Codex) or full plain-text payloads (Kimi, OpenCode, Hermes), so new conversations continue from established project history instead of starting cold. It handles installation across multiple agent apps, migration of project artifacts between checkout locations, and includes a build/verify pipeline (build-context.py, test.sh) for authoring canonical lore files like prompt.md, user.md, and lore.md.
github.comrepoAdded 22 Sep 2026, published 31 Aug 2026🧠 AI - Awesome Cybersecurity Agentic AI
A curated GitHub awesome-list cataloging the emerging agentic-AI security ecosystem: dozens of Model Context Protocol servers that give LLM agents access to security tools (Nuclei, Shodan, VirusTotal, Burp Suite, Ghidra, BloodHound, x64dbg), autonomous penetration-testing and CTF-solving agent frameworks (CAI, pentagi, BreachSeek, Dark-Moon, D-CIPHER), scanners/guardrails that audit agent skills, MCP servers, and multi-agent chains for prompt injection and other risks (Aguara, Inkog, MCP Doctor, AI-Infra-Guard, ATR), agentic SOC/detection platforms (Vigil), threat-modeling frameworks for agentic systems (MAESTRO, ATFAA/SHIELD), research papers, benchmark datasets, and community/learning resources. It functions as a living index for anyone building or defending AI-agent-driven security tooling.
github.comrepoAdded 3 Sep 2026, published 31 Aug 2026🛡️ Security - Dify
Dify is an open-source LLM application development platform combining a visual workflow builder, RAG pipeline, agent capabilities (with MCP server and tool integration), model management across hundreds of providers, and LLMOps observability. It offers both a hosted cloud service and self-hosted Community/Enterprise editions deployable via Docker Compose, aiming to take LLM apps from prototype to production with a backend-as-a-service API layer.
github.comrepoAdded 22 Sep 2026, published 31 Aug 2026🧠 AI - age
age is a simple, modern file encryption tool, format, and Go library by Filippo Valsorda and @benjojo, offering small explicit keys, no config options, UNIX-style composability, and now built-in hybrid post-quantum encryption (ML-KEM + X25519) as of v1.3.0. It supports multiple recipients, passphrase encryption, SSH key (ed25519/rsa) recipients/identities, hardware tokens via age-plugin-yubikey, and an age-inspect command to view encrypted-file metadata without decrypting.
github.comrepoAdded 3 Sep 2026, published 31 Aug 2026🛡️ Security - Mintplex-Labs/anything-llm
AnythingLLM is an open-source, MIT-licensed all-in-one LLM application from Mintplex Labs that lets users chat with their documents, run no-code AI agents, and connect to a wide range of LLM providers, embedders, vector databases, and TTS/STT services. It ships as a monorepo (frontend, server, collector, embed widget, browser extension) with multi-user permissioning, MCP compatibility, scheduled tasks, dynamic model routing, and both self-hosted (Docker) and desktop (Mac/Windows/Linux) deployment options.
github.comrepoAdded 23 Sep 2026, published 31 Aug 2026🧠 AI - Human-Agent-Society/reef
Reef is an open-source infrastructure stack for continual self-improving agents, wiring together agent inference, scored feedback, training/updates, and versioned delivery into one loop. It supports two learning surfaces: fine-tuning model weights via RL training steps (using Slime and SGLang on top of models like Qwen2.5-1.5B-Instruct) or evolving an agent's harness — prompts, rules, and skills — through its built-in "Reefine" recipe, which lets a model propose and install harness changes from plain-language requests. It exposes an OpenAI/Anthropic-compatible inference endpoint plus a reporting endpoint for scoring interactions, and ships a recipe catalog (e.g. the SAO recipe referencing arXiv:2607.07508) for pluggable learning strategies.
github.comrepoAdded 2 Oct 2026, published 31 Aug 2026🧠 AI - zhu1090093659/dsh-trading
dsh-trading is an open-source AI trading terminal built on "DeepSeek Harness" (DSH), a Cordis-based microkernel plugin ecosystem, covering crypto, US equities, China A-shares and Hong Kong stocks. Its notable design is a multi-agent team: a "master" lead agent grounds itself in a holdings ledger and user knowledge base, then decomposes work and delegates to persona-pinned subagents — a trader (trading plans/execution), an instrument-researcher (disclosures/fundamentals), and a risk-reviewer (exposure/stress scenarios) — each dispatching bundled domain "skills" and native tools for quotes, news, order books and backtesting. Every order defaults to dry-run simulation, live execution requires explicit opt-in plus interactive human approval, and headless sessions fail closed, illustrating a concrete human-approval-gated tool-use pattern for agentic systems.
github.comrepoAdded 2 Oct 2026, published 30 Aug 2026🧠 AI - emlai/defi-native-skill
An open-source Agent Skill ("defi-native") that teaches Claude Code, Cursor, Codex and other Agent-Skills-compatible agents capital-markets and DeFi domain knowledge, including yield decomposition, vault/curator anatomy, oracle classes, and stablecoin/RWA taxonomy. It is structured with progressive disclosure (SKILL.md routes to task-specific reference files only when needed), an api-routes.json router that forces live data pulls (vaults.fyi, DefiLlama, Morpho's GraphQL, rwa.xyz, Merkl, 130+ protocol docs) before any numeric claim, and a verified 90+ source manifest. The author describes an eval-gated release process (paired with/without-skill runs graded on structure) and adversarial review by independent models before publishing, making it a useful case study in skill engineering even for readers uninterested in DeFi itself.
github.comrepoAdded 2 Oct 2026, published 28 Aug 2026🧠 AI - baidu-baige/LoongSage
LoongSage is Baidu's open-sourced, production-grade reinforcement learning framework for post-training LLMs, built on Ray for scheduling, Megatron-Core/Megatron-Bridge for training, and SGLang for inference. It targets agentic RL with a zero-intrusion AgentFlow module (automatic multi-turn context, loss masking, trajectory collection), multi-paradigm online distillation (PG-Style, GKD-Style, TopK/full-vocab/JSD KL), fully asynchronous training with partial rollout, and system-level training-inference consistency guarantees (Router Replay, TITO, M2PO, OPSM) that keep probability bias at 1e-4 in MoE/low-precision settings. Recipes are validated on Baidu's internal production runs of DeepSeek-V4-Flash and Qwen3-30B-A3B for math reasoning, agentic code repair, and distillation.
github.comrepoAdded 30 Sep 2026, published 28 Aug 2026🧠 AI - vibecheck
vibecheck is a free, open-source, client-side scanner that checks apps built with AI code generators (Lovable, Bolt, v0, Cursor, Claude Code) for common security holes: exposed Supabase Row Level Security / Firebase rules, secrets embedded in the client bundle (Stripe/AWS/DB keys), missing security headers, exposed .env/.git/source maps, unauthenticated LLM proxy or MCP endpoints, and email/TLS misconfigurations. It also scans public repos for cross-tenant IDOR patterns, committed secrets, an OSV.dev supply-chain check, a Dockerfile lint, and generates a CycloneDX SBOM; a companion CLI (tenant-guard) adds a live Postgres cross-tenant isolation test as a CI gate. The project cites CVE-2025-48757 (170+ Lovable apps found with RLS disabled) as motivation.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - numasec
numasec is an open-source AI security agent that runs in the terminal, wrapping a user-chosen LLM (OpenAI, Anthropic, Google, Bedrock, Ollama, etc.) with an operation kernel that tracks target scope, runbooks, findings, evidence, replay, and reports across a security engagement. It orchestrates local tools such as nmap, sqlmap, ffuf, gobuster, nikto, nuclei, trivy, and checksec, and is aimed primarily at authorized AppSec triage and Pentest workflows, with OSINT, CTF, and cloud surfaces marked as less mature.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - DataSentry
DataSentry is a Claude Code plugin that redacts secrets (AWS keys, tokens, credentials) from tool outputs before they enter the model's context window, using deterministic hooks rather than model instructions, and blocks prompts that contain live credentials. It ships 40 regex-based detection rules (ported from an enterprise Warp ADE ruleset), stable per-secret placeholders via sha1 hashing, per-category overrides, an audit log, and a fail-closed mode; PII/financial/healthcare pattern detection is reserved for a paid Enterprise tier.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - CrystalPotato
CrystalPotato is a Crystal-language port of GodPotato, a Windows local privilege escalation tool that abuses the DCOM OXID Resolver and named pipe impersonation to escalate from an account with SeImpersonatePrivilege to SYSTEM. It resolves Windows APIs dynamically, invokes them via indirect syscall stubs, XOR-obfuscates strings at compile time, and can execute commands, spawn reverse shells, or create a local admin account. Compiles to a single dependency-free static binary and was tested on Windows 10, 11, and Server 2025.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - YesWeHack Claude Kit
Claude Kit is a Claude Code plugin from YesWeHack that helps bug bounty hunters draft and triage vulnerability reports without letting the AI invent unverified technical details. It adds an always-on SessionStart hook enforcing evidence-only claims (no theoretical impact, no OWASP boilerplate padding) plus three on-demand skills (/ywh:write, /ywh:triage, class-specific checks) that structure findings, flag unproven claims, and recompute defensible CVSS scores — e.g. downgrading an inflated 9.1 to ~5.9 Medium after verifying an IDOR's actual exploitability (AC:H, non-enumerable UUIDv4 ID).
github.comrepoPublished and added 27 Aug 2026🛡️ Security - BountySkiller
BountySkiller is a Flask app with two bug-bounty-focused tools: a collector that pulls disclosed HackerOne hacktivity and bug-bounty writeups (plus RSS/Google sources) into local JSON, and "Hunt Buddy," a browser-driven orchestrator that takes a target profile, runs a gap analysis against a set of pluggable bug-class hunting modules (sourced from an external HUNT_TOOLS directory, e.g. SSRF), and produces ranked findings with per-module status and enforced scope.domains restrictions. It exposes a small REST API (/api/hunt/plan, /api/hunt/run, /api/fetch, etc.) for scripting the collection and hunt workflow.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - subScraper
subScraper is a self-contained, single-file (main.py) Python orchestrator that chains subdomain enumeration tools (Amass, Subfinder, Assetfinder, Findomain, Sublist3r) into httpx probing, screenshot capture, ffuf fuzzing, nuclei, and nikto scans, all driven from a live web UI with resumable job state, worker concurrency controls, and Docker packaging. It ships 34 custom nuclei templates for CVEs lacking official coverage and exposes a scoped, API-key-authenticated "bug bounty agent API" for programmatic recon and attack-surface queries against a target's scope.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - ThreatRadar
ThreatRadar is an open-source, Docker-based threat intelligence pipeline that ingests IOCs from feeds like NVD, OTX, AbuseIPDB, and EmergingThreats, enriches them with MITRE ATT&CK and CVSS data, and scores them via Cortex analyzers (VirusTotal, AbuseIPDB, Maltiverse, IPinfo, Urlscan, HybridAnalysis). Its core focus is feed poisoning detection: a scikit-learn IsolationForest model flags statistically anomalous IOCs, which are then semantically validated by an LLM (GPT-4o via OpenRouter) against eight contradiction classes (e.g., APT-sector mismatches) before enriched, validated intel is pushed to MISP with TLP tagging, and analyst-confirmed sightings feed back into retraining the anomaly model.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - Rekono
Rekono is an open-source pentesting automation platform that chains 19 hacking tools (Nmap, Nuclei, Metasploit, OWASP ZAP, Nikto, Gitleaks, SearchSploit, etc.) so that output from one tool feeds the next, automatically covering recon, service enumeration, vulnerability scanning, and exploit correlation. It deduplicates findings into a single attack-surface inventory per host/port, enriches CVEs with community context for prioritization, tracks fixed/reopened vulnerabilities, and supports team collaboration, scheduled scans, Telegram/email alerts, and report generation for engagements.
github.comrepoAdded 3 Sep 2026, published 27 Aug 2026🛡️ Security - S1N6H/pentest-harness
pentest-harness is an open-source, plugin-based AI agent framework aimed at authorized penetration tests, bug bounty research, security labs, and CTFs. It provides a "Pentest Mode" offensive-security operating standard, a full agent toolset (shell, filesystem, web research, subagents, background jobs), and a bring-your-own-key multi-provider LLM engine (OpenAI, Anthropic, DeepSeek, Google, Mistral, Groq, OpenRouter, Azure OpenAI) with durable JSONL/SQLite session persistence and an owner-only credential store for API keys.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - whitecircle/halo
Halo is White Circle's open-source training framework that runs the same codebase from a single GPU to multi-node clusters, adding Expert/Context/Tensor/Expert-Tensor parallelism (EP/CP/TP/ETP) directly onto native Hugging Face models via FSDP2, DTensor and DeviceMesh rather than a separate distributed model implementation. It covers the full training lifecycle — pre-training, SFT, preference optimization, distillation, and fully asynchronous multi-turn RL with a Transformers-side trainer pushing weights over NCCL to vLLM/SGLang rollout servers — and reports up to 2.8x the throughput of stock TRL for gpt-oss-20b on 8x B300 GPUs. It ships as prebuilt Docker images for Blackwell and Hopper GPUs with FlashAttention-4, DeepEP V2, DeepGEMM, and a bf16 AdamW optimizer integrated, supports 15 MoE families, and includes LoRA/QLoRA paths that fit consumer GPUs.
github.comrepoAdded 30 Sep 2026, published 26 Aug 2026🧠 AI - IAM Policy Autopilot
IAM Policy Autopilot is an AWS Labs open-source CLI/MCP server that statically analyzes application source code (Python, Go, TypeScript, JavaScript, Java) or a Terraform plan JSON to generate baseline least-privilege IAM identity-based policies, and can also parse AccessDenied error messages to suggest policy fixes. It integrates with AI coding assistants (Kiro, Claude Desktop, etc.) via MCP so assistants can auto-generate scoped IAM permissions instead of overly broad ones, with a --service-hints flag to reduce false-positive permission inclusion.
github.comrepoPublished and added 25 Aug 2026🛡️ Security - Cyberful
Cyberful is an AI red-team CLI that orchestrates 316 cybersecurity tools (203 CLI apps/commands including Nmap, Metasploit, Nuclei, plus ZAP and Ghidra) through a multi-agent system: hypothesis workers map attack surfaces and test exploit paths, while a deterministic control plane enforces engagement scope, preserves evidence, and only surfaces independently reproduced vulnerabilities. Built for authorized penetration testing, code audits, and bug bounty hunting; ships a hardened agent-controlled browser, Docker-based runtime, offline MITRE ATT&CK snapshot, and CVE dictionary.
github.comrepoPublished and added 25 Aug 2026🛡️ Security - Ashmmmm/crockTail
crockTail is a passive OSINT tool that, given a domain, aggregates DNS records, IP/ASN ownership, TLS certificate details, WHOIS data, and crt.sh certificate-transparency history into a single report. It layers analysis on top of the raw data: plain-language warning/info observations (near-expiry or expired certs, recently registered domains, unusual reissuance, historical subdomains from CT logs), multi-resolver (Google vs Cloudflare) DNS cross-verification to flag possible tampering, and a 0-100 confidence score per scan based on module success and cross-check agreement. It supports batch domain queries and query logging, and is explicitly limited to passive lookups and a standard TLS handshake, no port scanning or active probing.
github.comrepoAdded 30 Sep 2026, published 25 Aug 2026🛡️ Security - henrymao2004/Auto-research-red-teaming
AHA (Agent Hacks Agent) is an autonomous red-teaming framework where a researcher agent iteratively hypothesizes attacks, runs them against Docker-sandboxed victim agents (built on Claude Code and Codex, targeting frontier models like Minimax-M2.7, Kimi-K2.6, and Deepseek-V4-Pro), and accumulates a persistent Vulnerability Concept Graph of reusable attack mechanisms rather than one-off jailbreak strings. It reports held-out Attack Success Rate evaluations showing these mechanisms — notably a "claimed-authorization" bypass pattern — transfer across scenarios and victim models (up to ~88% of native ASR), and ships as registry-discovered plugins for scenarios like AgentHazard, AgentDojo-style indirect injection, and DecodingTrust-Agent.
github.comrepoPublished and added 25 Aug 2026🛡️ Security - Cloudflare Computer
Cloudflare Computer is a preview virtual filesystem living inside a Durable Object, with authoritative state in SQLite exposed through three pluggable execution backends: a full Linux container mounted via FUSE and capnweb RPC, an isolated shell (just-bash) running in a Dynamic Worker, and isolated JavaScript modules in a fresh Dynamic Worker with scoped fs/git/artifacts access. It's designed as sandboxing infrastructure for AI agents, with examples demonstrating per-backend egress policy controls (none/all/custom) and MCP-based code execution tools, making it relevant to securely isolating and constraining agent/LLM code execution.
github.comrepoAdded 3 Sep 2026, published 25 Aug 2026🛡️ Security - ADScanPro/Claude-AD
Claude-AD is a Claude Code plugin that packages Active Directory pentest methodology as skills, agents, and slash commands, directing Claude to run standard tooling (netexec, Impacket, certipy, bloodyAD, BloodHound CE) in the correct setup-collection-exploitation-post order. It covers environment constraints that break tooling in hardened domains (AES-only Kerberos, LDAP channel binding, Protected Users, LAPS, gMSA), techniques like Kerberoasting, AS-REP roasting, ADCS ESC1-ESC17, ACL abuse, coercion/NTLM relay (PetitPotam, PrinterBug, DFSCoerce) and delegation abuse with their Windows Event IDs/MDI telemetry, and maps each technique to DORA/NIS2/ENS compliance controls. Exploitation agents require human confirmation before directory-modifying actions.
github.comrepoAdded 2 Oct 2026, published 24 Aug 2026🛡️ Security - flawed
flawed is a static-analysis engine for Python web applications that builds a framework-aware model of an app's routes, request inputs, state effects, call graph, and value flow, exposing it both as a queryable Python library (open_repo(), load_findings()) and a CLI scanner. It runs pluggable rule modules (@detector contract) across three layers — L1 index, L2 semantic model, L3 rules — and outputs findings as JSON/SARIF with baseline diffing support for CI use.
github.comrepoPublished and added 23 Aug 2026🛡️ Security - agentgg
agentgg is an open-source, agentic SAST scanner that uses LLM agents to read source code, follow imports, trace the call graph, and confirm findings before reporting — aiming to reduce the pattern-matching false positives of traditional SAST. It runs locally or as a hosted service, supports full-repo scans or git-diff PR review, and works with multiple model providers (Anthropic, OpenAI, AWS Bedrock, Google Vertex AI, OpenRouter, Ollama); agents are defined as markdown files with YAML frontmatter and are pulled from a community agents catalog.
github.comrepoPublished and added 23 Aug 2026🛡️ Security - Cybermes
Cybermes is an open-source bug bounty and pentest automation framework that pairs a native Go MCP server (cybermes-mcp) with an autonomous Hermes CLI agent, orchestrating recon tools (subfinder, httpx, katana, ffuf, Nuclei, sqlmap), 200+ offensive playbooks covering IDOR/BOLA, JWT, SSRF, XSS, SQLi and cloud misconfig, and a validation-gate workflow that writes non-destructive PoC scripts before compiling findings into Markdown/HTML/PDF reports. It exposes its tools over JSON-RPC 2.0 to AI coding assistants (Claude Desktop, Cursor, Windsurf, Cline, Gemini/Antigravity) so an external LLM can drive scoped, evidence-backed security assessments.
github.comrepoPublished and added 23 Aug 2026🛡️ Security - duty1g/x64dbg-mcp-server
x64dbg-MCP Server is a native, dependency-free Zig plugin for the x64dbg debugger that exposes 84 MCP tools and 22 event callbacks over Streamable HTTP and SSE transports, letting any MCP-compatible AI assistant drive breakpoints, stepping, memory reads/writes, register and stack inspection, pattern scanning, PE analysis, and module dumping. It implements the MCP 2024-11-05 spec with JSON-RPC 2.0, mandatory bearer-token auth, a Win32 config dialog, and cross-compiles to both x32 and x64 from a single codebase. The project targets AI-assisted reverse engineering and malware-analysis workflows, turning a traditional interactive debugger into an agent-controllable backend.
github.comrepoAdded 2 Oct 2026, published 22 Aug 2026🧠 AI - duty1g/x64dbg-mcp-server
x64dbg-MCP Server is a native, zero-dependency MCP plugin (built in Zig) for the x64dbg Windows debugger that exposes its full API — breakpoints, stepping, memory allocation/read/write, registers, modules, threads, call stack, pattern scanning, xrefs, symbols, PE/OEP analysis and module dumping — as 84 MCP tools plus 22 event callbacks over Streamable HTTP and SSE transports with mandatory bearer-token auth. It lets any MCP-compatible AI assistant drive an interactive reverse-engineering session against a running process (e.g. load a binary, set a breakpoint, dump registers, step and inspect the stack) directly from inside x64dbg's address space, with no polling or external process required.
github.comrepoAdded 2 Oct 2026, published 22 Aug 2026🛡️ Security - Deep Eye
Deep Eye is an open-source Python pentesting framework that orchestrates 11 AI providers (OpenAI, Claude, Grok, Gemini, Ollama, Groq, Mistral, OpenRouter, LiteLLM, LM Studio, and more) with automatic failover to generate context-aware attack payloads for 50+ vulnerability classes including SQLi, XSS, SSRF, IDOR, JWT and GraphQL flaws. It adds an RAG-indexed CVE intelligence DB built from NVD/MITRE/Exploit-DB, AI-based finding triage and false-positive filtering, Nuclei-style YAML templates, Playwright browser automation, CAPTCHA-solving (reCAPTCHA/hCaptcha/Turnstile/Arkose), mitmproxy interception, and auto-generated HackerOne-style bug bounty reports with PCI-DSS/SOC2/ISO 27001 compliance mapping, SARIF/JUnit export, scan diffing, and retest workflows.
github.comrepoAdded 3 Sep 2026, published 22 Aug 2026🛡️ Security - MinIO Security Lab
A defensive security review lab for MinIO pinned at commit 7aac2a2 (~RELEASE.2025-10-15+11), providing Docker-based single-node, two-node replication, and dual-OIDC environments plus per-finding repro.sh PoCs for issues including service-account key path traversal, server-update SSRF, cross-provider OIDC token acceptance, source-IP/X-Forwarded-For trust, tag-deletion replication bypass, batch job data exfiltration, and secrets exposed via config history. Each of 16+ findings (F-01 through F-16) has ANALYSIS.md with root cause, data-flow trace, and suggested fix, produced via a generate/judge/independent-verify pipeline with cross-vendor adjudication (including an OpenAI/codex-based verifier) and live validation on a lab-built Go binary; ~90 candidates were triaged with ~55 set aside as false positives or intended behavior.
github.comrepoAdded 3 Sep 2026, published 21 Aug 2026🛡️ Security - Teycir/BurpAPISecuritySuite
BurpAPISecuritySuite is a Jython-based Burp Suite extension that consolidates API reconnaissance, intelligent fuzzing (108+ payloads across 15 attack types including BOLA, IDOR, JWT exploitation, GraphQL abuse, SSTI, and WAF bypass), and passive deep-logic checks (counterfactual differentials, sequence invariants, token lineage, cross-interface parity drift) into a single tool covering the OWASP API Top 10. It auto-captures and normalizes API traffic, exports attack campaigns to Burp Intruder/Turbo Intruder/Nuclei, and generates AI-ready bundles (ChatGPT/Claude/Ollama) for LLM-assisted triage, while orchestrating external tools like ApiHunter, Katana, httpx, FFUF, Kiterunner, sqlmap, and Dalfox for verification.
github.comrepoPublished and added 21 Aug 2026🛡️ Security - CarterPerez-dev/Cybersecurity-Projects
A GitHub repo of hands-on cybersecurity build projects with full source code, organized into Foundations (pre-beginner, heavily commented single-file Python teaching projects), Beginner, Intermediate, and Advanced tiers, including a work-in-progress DDoS mitigation tool. It also bundles 10 certification/career roadmaps (SOC Analyst, Pentester, Security Engineer, GRC Analyst, etc.) and a curated list of learning tools, courses, and communities, cross-promoting the author's CertGames platform for guided versions of the same projects.
github.comrepoPublished and added 21 Aug 2026🛡️ Security - SKANF
SKANF is a static and symbolic analysis tool that finds asset-management vulnerabilities in closed-source or obfuscated EVM smart contracts by fetching deployed bytecode from a JSON-RPC endpoint and locating attacker-reachable sensitive external calls (e.g. ERC-20 transfer/transferFrom/approve on tokens like USDT or WBTC). Beyond detection, it includes an exploit-generation phase that symbolically synthesizes calldata satisfying a verified vulnerability's preconditions and replays it against a forked EVM to confirm real balance changes. It builds on custom forks of the greed symbolic execution engine and the Gigahorse decompiler, and accompanies the ACM CCS 2026 paper "Insecurity Through Obscurity: Veiled Vulnerabilities in Closed-Source Contracts."
github.comrepoPublished and added 21 Aug 2026🛡️ Security - archcanary
Archcanary is a read-only, layered detection scanner for Arch Linux (and derivatives like EndeavourOS/Manjaro) that checks installed packages, pacman logs, systemd units, eBPF programs, ld.so.preload, DKMS kernel modules, and npm/bun/yarn/pnpm caches against curated and third-party (aur-audit.wtako.net) threat lists. It was built in direct response to a 2026 AUR supply-chain attack in which commit forgery was used to impersonate maintainers and inject npm/bun install hooks delivering an infostealer (Discord tokens, GitHub PATs, SSH keys, Vault tokens) and a CAP_BPF eBPF rootkit into 1600+ PKGBUILDs, plus a separate Russian-spam PKGBUILD injection campaign. It integrates with yay/paru pre-build hooks, systemd timers, auditd, and Lynis, and originated as a fork/expansion of lenucksi/aur-malware-check.
github.comrepoPublished and added 21 Aug 2026🛡️ Security - ScreenshotDetector
ScreenshotDetector is an Android app-layer tool that detects screenshot, screen recording, screen mirroring, and casting activity using a combination of public APIs (ScreenCaptureCallback, ScreenRecordingCallback, DisplayManager, MediaProjection, ContentObserver/MediaStore, FileObserver, AccessibilityService, NotificationListenerService) and hidden APIs accessed via reflection (DisplayManagerGlobal.getDisplayInfo, WifiDisplayStatus, AppOps project_media/project_audio). It is positioned as a research counterpart to ScreenshotFaker (an LSPosed/Shizuku-based tool that forges/bypasses screenshot detection), illustrating the attacker/defender dynamic around screen-capture evasion on Android, including detection of adb shell screencap/screenrecord, freeform/mini-window attribution, and accessibility-overlay/screen-reader channel abuse detection.
github.comrepoPublished and added 21 Aug 2026🛡️ Security - Uber ADR (Agentic AI Detection and Response)
ADR (Agentic AI Detection and Response) is Uber's open-source enterprise security system for AI agents, covering discovery of unsanctioned AI tools on endpoints, telemetry capture of agent intent/tool-use/execution traces, a benchmark (ADR-Bench: 300+ tasks, 134 MCP servers, 17 agent attack techniques), and a dual-agent detector for risky agent behavior. It is deployed in production at Uber to secure employee-facing coding agents (Cursor, Claude Code, Codex, GitHub Copilot CLI, DeepSeek) and customer-facing support agents; the accompanying paper was accepted to MLSys 2026. The prevention component and offline red-teaming engine (ADR Explorer) are not included in the open-source release.
github.comrepoPublished and added 21 Aug 2026🛡️ Security - Superior-Trade/trading-terminal
Open-source (Apache-2.0) AI trading terminal for Hyperliquid where a user sketches a chart read (trendlines, levels, fib retracements) and an agent turns it into a ranked trade setup with entry, stop and target, then generates a Freqtrade Python strategy to trade it. The generated strategy passes through a validator that catches unsafe patterns and sends failures back to the model in a repair loop until the code is safe to deploy, a pattern documented in docs/strategy-pipeline.md. It is self-hostable or available as a hosted build, and also exposes an agent-facing entry point (SKILL.md) for coding agents like Claude Code, Codex and Cursor to trade directly without the UI.
github.comrepoAdded 2 Oct 2026, published 21 Aug 2026🧠 AI - Orbien
Orbien is a lightweight (~5MB binary) NAT traversal / intranet penetration tool written in Rust with Tokio, supporting tunnel protocols (TCP, UDP, HTTP, HTTPS, SOCKS5) over multiple transports (TCP, KCP, WebSocket, QUIC). It provides token-based tunnel authentication and TLS/mTLS encryption, positioning it as a secure, high-performance alternative to frp for exposing internal services or pivoting through NAT.
github.comrepoAdded 3 Sep 2026, published 21 Aug 2026🛡️ Security - armourinfosec/Offensive-Linux-Privilege-Escalation
A structured collection of 50+ notes taking a low-privileged Linux foothold to root, covering sudo/SUID misconfigurations, GTFOBins and LD_PRELOAD abuse, the Baron Samedit sudo bug, Linux capabilities, cron/systemd-timer abuse, kernel exploits (DirtyCow, DirtyPipe, OverlayFS, PwnKit), NFS no_root_squash, Docker/LXD namespace escapes, screen/tmux and D-Bus IPC abuse, and credential mining. Each note follows a concept-to-exploitation-to-detection-to-defense format and the repo includes a methodology checklist, hardening guide, two guided labs with a lab-setup script, and skills assessments, published for authorized lab/CTF use under CC BY 4.0.
github.comrepoAdded 2 Oct 2026, published 19 Aug 2026🛡️ Security - 0sec-labs/0
"0" is an open-source security workflow runner from 0sec Labs (YC-backed, with a Swiss Applied AI & Cybersecurity Research Lab) usable from a terminal, a browser "Command Center," or a coding agent via MCP. It ships 12 starter templates (e.g. a "security-research" template that produces a source review of a demo API with code locations and suggested fixes), supports scheduled/triggered runs with retained results and revision history, and integrates with GitHub, Elastic, Semgrep, Snyk, Linear, Jira, Cloudflare, Slack and Teams via plugins.
github.comrepoAdded 2 Oct 2026, published 19 Aug 2026🛡️ Security - keli-wen/agy-staff
agy-staff is a plugin that lets Claude Code, Codex, Pi and OpenCode delegate work to Google's Antigravity CLI (agy), which runs Gemini 3.8 Flash. It provides five personas (staffer, researcher, reviewer, implementer, ask), a lead orchestration skill and a jobs skill for background tasks. Its Bench v1 compared solo, own-subagent and agy runs on three benchmarks: agy cut Claude Code's host spend by 16% to 50% but raised median task time from 2 to 8 minutes to 13 to 26 minutes.
github.comrepoAdded 20 Oct 2026, published 18 Aug 2026🧠 AI - yetone/cumora
Cumora is a cross-platform team-chat application where AI agents sit alongside humans as first-class participants — holding persistent personas and memory, claiming Kanban work, coordinating with each other, and sending real email — rather than only responding when addressed. Agents can run on Cumora's cloud (per-agent Kubernetes pods driving a multi-hop tool-calling loop over the OpenAI Responses API) or in "Bring Your Own Agent" mode, pairing a local Mac/VPS daemon with an existing coding-agent backend (Claude Code, Codex, Cursor Agent, Gemini CLI, OpenCode, Qwen Code, Google Antigravity, etc.) while keeping provider keys off the server. The repo documents a concrete coordination design — a seen-cursor freshness gate that holds stale replies, atomic claims on units of work, a small-brain triage gate, and a transactional Postgres outbox for realtime fan-out — making it a useful reference for building multi-agent systems that avoid agents colliding on shared work.
github.comrepoAdded 30 Sep 2026, published 17 Aug 2026🧠 AI - hunt.md
hunt.md is an open, portable Markdown format for writing threat-hunting playbooks as git-diffable documents combining YAML frontmatter with a typed graph of steps — queries, data collection, agent reasoning, human review, and response. The reference tool huntmd validates hunts (checking reachability, variable use, agent bounds, gated destructive actions) and converts between hunt.md, Huntbase definitions, OASIS CACAO v2 playbooks, and MISP events, with CACAO round-trip tested against 49 real playbooks from six projects.
github.comrepoAdded 3 Sep 2026, published 17 Aug 2026🛡️ Security - galleonlabs/hypergrok-trading-desk
HyperGrok Trading Desk is an open-source "Agent Skills" pack (MIT licensed) that turns a Grok Bot, Claude Code or Cursor instance into a coordinated seven-agent trading desk for Hyperliquid perpetuals, using seventeen portable SKILL.md skills covering bootstrap/setup, exchange API access, and desk operating procedures. Each trade moves through a fixed pipeline — idea, evidence, risk sign-off, explicit human approval by ticket id, a single execution agent that sends the order, reconciliation, and a separate review agent — with read-only "opening bell" and "desk doctor" scripts for zero-key market snapshots and release/connectivity checks. The design choices worth noting for agent builders are the one-writer/many-readers pattern, sizing risk off the stressed (slipped) cost of a stop rather than its trigger price, and keeping the approval gate (Grok Bot's Require Approval rule) outside the chat the agent itself can write to.
github.comrepoAdded 5 Oct 2026, published 16 Aug 2026🧠 AI - opaxial/CVE-2026-9830
A Python proof-of-concept (CVE-2026-9830) that validates an unauthenticated REST API exposure in the BookingPress Pro WordPress plugin, where unauthenticated requests to a booking endpoint can return customer PII such as names, emails, phone numbers, and booking details. The script supports non-invasive checking, proxy/timeout/user-agent configuration, booking ID and date filtering, and optional saving of retrieved responses, alongside guidance for responsible use and remediation (patching, enforcing auth/capability checks on REST routes, log review, and incident response).
github.comrepoAdded 2 Oct 2026, published 15 Aug 2026🛡️ Security - vscan
vscan is an open-source, lightweight, cross-platform website vulnerability scanner built for authorized security assessments. It combines port scanning and fingerprint identification (using a merged database of ~6,832 fingerprints from eHole, wappalyzergo, and local rules), login credential brute-forcing, sensitive file detection, and vulnerability PoC checks compatible with both Xray and Nuclei PoC formats. It supports flexible input (STDIN/host/IP/CIDR/URL/TXT) and output formats (JSON/TXT/CSV/STDOUT).
github.comrepoPublished and added 15 Aug 2026🛡️ Security - ITScape / Januscape / Zapscape
ITScape is a guest-to-host escape exploit (CVE-2026-46316) against KVM/arm64, discovered by Hyunwoo Kim (@v4bel), exploiting a race condition in the vGIC-ITS (Interrupt Translation Service) emulation inside the Linux kernel's in-kernel KVM code rather than QEMU userspace. A malicious guest with only EL1 (guest kernel) privilege can trigger the bug via GIC/ITS MMIO to gain host kernel (root) code execution, threatening isolation on multi-tenant arm64 public clouds; the repo includes a reproducible PoC built on the Linux kvm selftest framework and QEMU TCG for safe testing, plus patch/version range and disclosure timeline.
github.comrepoPublished and added 15 Aug 2026🛡️ Security - Andrej Karpathy Skills
A single CLAUDE.md file (also packaged as a Claude Code plugin and Cursor rule) that encodes four principles derived from Andrej Karpathy's public observations on LLM coding failure modes: surfacing assumptions and ambiguity instead of silently guessing, avoiding overengineered/bloated code, touching only what's necessary when editing, and using verifiable success criteria for goal-driven execution loops. It's distributed as a drop-in instructions file, a Claude Code marketplace plugin, and a committed Cursor project rule.
github.comrepoAdded 22 Sep 2026, published 15 Aug 2026🧠 AI - Nothing Private
Nothing Private is a PHP/MySQL proof-of-concept that uses the ClientJS browser-fingerprinting library to generate a persistent device fingerprint from attributes like user agent, screen resolution, plugin list, font list, timezone, and canvas print, storing it alongside a user-submitted name. It demonstrates that the same fingerprint (and thus identity) can be matched even after switching to private/incognito mode, showing that clearing history does not prevent server-side tracking via fingerprinting.
github.comrepoAdded 3 Sep 2026, published 14 Aug 2026🛡️ Security - MakazhanAlpamys/Soup
Soup is a CLI tool for fine-tuning and post-training LLMs with a single YAML config and one command, wrapping transformers/PEFT/TRL/MLX backends with auto batch-size/GPU detection and QLoRA support. Its notable technical contribution is "layer streaming," which trains an 8B model on a 4GB laptop GPU by streaming the frozen base model from host RAM one decoder layer at a time, verified bit-exact against resident runs and documented in an accompanying Zenodo preprint with detailed benchmark data including failures and retracted claims.
github.comrepoAdded 22 Sep 2026, published 14 Aug 2026🧠 AI - VaultKeepR/vaultkeepr-public
vaultkeepr-public is the MIT-licensed repository behind VaultKeepR, a zero-knowledge password manager. It holds 15 SDK packages published to npm under @vaultkeepr and Solidity contracts on Base L2 that anchor vault locations, recovery fragments and digital legacy, tested with Foundry. Encryption is XChaCha20-Poly1305 with Argon2id (t=3, m=64 MiB, p=4), and docs/THREAT_MODEL.md covers assets, adversaries and trust boundaries. Clients stay in a private repository.
github.comrepoAdded 23 Oct 2026, published 12 Aug 2026🛡️ Security - Cariddi
Cariddi is a Go-based CLI tool that crawls a list of domains/URLs to discover endpoints, secrets, API keys, tokens, and juicy file extensions. It supports proxying through Burp Suite, custom headers, secret/endpoint regex files, JSON/HTML/TXT output, and configurable crawl depth and concurrency, making it a common recon tool in bug bounty and pentest workflows.
github.comrepoAdded 3 Sep 2026, published 12 Aug 2026🛡️ Security - calmrocks/ai-engineer-notebooks
A GitHub repo of self-contained, runnable Colab notebooks teaching the AI Engineer / Forward Deployed Engineer skill set from raw model APIs rather than frameworks like LangChain. It covers model APIs, evals (treated as central rather than an afterthought), RAG, agents (loop from scratch, tool design, guardrails, MCP), LoRA fine-tuning, security, operations, and serving/inference performance, all runnable free on the Groq API with optional Colab-GPU appendices for GPU-only topics. Includes real end-to-end case studies and a capstone project brief aimed at people moving from backend/full-stack roles into applied AI roles.
github.comrepoAdded 23 Sep 2026, published 11 Aug 2026🧠 AI - xiaoyeuzixi/revlab
REVLab is a Windows-local binary analysis workbench for PE files, Unreal Engine dumps and Unity game folders. Its graph workflow engine runs LLM analysis nodes as tool-calling operators: up to 6 tool rounds by default, a target path locked by the workflow, a saved tool_trace, and a read-only fallback when the gateway lacks tools support. Evidence is labelled static, runtime, inferred or blocked, and model output is capped at ai_inferred. An MCP server lets external agents read evidence and submit conclusions.
github.comrepoAdded 23 Oct 2026, published 11 Aug 2026🧠 AI - xiaoyeuzixi/revlab
REVLab is a local Windows binary analysis workbench covering generic PE files, Unreal Engine dumps and Unity game directories. It splits work into stages (identify, unpack, disassemble with Capstone, decompile with Ghidra Headless, gated local dynamic run) stored per sample in SQLite. A Vue Flow workflow editor, AI tool-loop nodes and an MCP server let external agents drive analysis, with evidence labelled static, runtime, inferred or blocked.
github.comrepoAdded 23 Oct 2026, published 11 Aug 2026🛡️ Security - aliang-one/aliangboard
AliangBoard is an open-source Kubernetes management panel with a built-in LLM agent workbench and an MCP server (Streamable HTTP, API-key auth). Tools are tiered read, operator and admin, each key is bound to a ServiceAccount, writes need human approval, and calls are audited. The agent uses any OpenAI-compatible endpoint, and Claude Code can connect over MCP. It also covers multi-cluster management, exec, port-forward and SSH servers.
github.comrepoAdded 19 Oct 2026, published 11 Aug 2026🧠 AI - FareedKhan-dev/kimi-k3-in-c
A GitHub project implementing inference for the 2.78-trillion-parameter Kimi K3 model entirely in portable C99, running on a single CPU with just 8.24 GB of RAM — no BLAS, no ML framework, no GPU required. It demonstrates extreme memory-efficient quantization and low-level serving techniques for running massive models on commodity hardware.
github.comrepoAdded 22 Sep 2026, published 10 Aug 2026🧠 AI - sgkdev/bad_garbage
GitHub repo (sgkdev/bad_garbage) containing a proof-of-concept exploit for CVE-2026-53361, an unprivileged, container-escapable use-after-free in the Linux AF_UNIX socket garbage collector. The bug stems from a race where a concurrent MSG_PEEK on an in-flight socket slips past the gc_in_progress check, letting the GC free a still-referenced socket; the same underlying race has been patched three separate times (CVE-2021-0920, CVE-2026-23394, CVE-2026-53361). The PoC targets systems with 2–7 CPUs and notes that most SLUB cache-armoring/shadowing code was stripped out, leaving occasional collisions in kmalloc-64/anon_vma caches that a user would need to re-armor for near-100% reliability.
github.comrepoAdded 2 Oct 2026, published 10 Aug 2026🛡️ Security - AuditSentry
AuditSentry is a GitHub project that pairs Claude Code with 13 specialized MCP servers and 23 parallel AI agents to audit Solidity and Vyper smart contracts, generating vulnerability findings, working exploit PoCs, mainnet-fork simulations, and CVSS-scored audit reports. It targets DeFi-specific bug classes (reentrancy, oracle manipulation, flash loan attacks, ERC-4626 inflation, cross-chain messaging replay, L2 sequencer issues, ERC-4337 account abstraction) and claims results benchmarked against 150+ historical Code4rena/Sherlock contest findings.
github.comrepoAdded 3 Sep 2026, published 10 Aug 2026🛡️ Security - Armada
Armada is a CLI tool (npm package @rafamacalaba/armada) that turns a repository into a multi-agent "fleet" of 8 specialist AI roles (developer, QA, security, adversary, architect, Commodore orchestrator, etc.) built on opencode. It implements "loop engineering": a contract-driven control loop (contract → dispatch → build → test → review → PR) with maker/checker separation, parallel phase dispatch in isolated git worktrees, evidence-gated transitions, and crash-proof on-disk state, aiming to replace unsupervised one-shot agent prompting with a verified, resumable workflow that lands a reviewed PR.
github.comrepoAdded 22 Sep 2026, published 10 Aug 2026🧠 AI - Leonxlnx/unlazy
unlazy is an agent skill for Claude Code, Codex CLI and other agent harnesses that enforces "completion discipline": before AI-agent work is reported done, it must satisfy a ledger of runnable gates (GATES.md) whose shell/Node checks are executed and whose output must match a declared EXPECT: string, with digest-bound evidence, approval records, and --reverify to re-run already-"complete" gates. It also provides scoped multi-leaf/branch orchestration with lease-based claiming for parallel agent dispatch, a Claude Code Stop-hook that blocks premature completion, and documentation of the threat model (shell resolution, PATH, approval storage) around executing arbitrary checker commands. The README grounds the design in cited research on LLM laziness, premature truncation, and over/under-thinking (e.g. METR's Time Horizon, SlopCodeBench, OptimalThinkingBench, s1), while being explicit that this research motivates but does not prove the tool's effectiveness.
github.comrepoAdded 2 Oct 2026, published 9 Aug 2026🧠 AI - HarnessRouter/harnessrouter
HarnessRouter is a self-hostable (Docker) infrastructure layer that wraps existing agent harnesses such as Codex and Claude Code behind one OpenAI Responses-compatible API, letting a product run tasks, stream progress, manage files/artifacts, and switch harnesses without writing harness-specific integration code. It implements the Unified Harness Protocol (UHP), a versioned, OpenAI Responses-compatible contract with a reference implementation, schemas, and conformance suite, plus features like per-session workspaces, custom harness configuration with tools/skills/MCP servers, and secret redaction via vault references or header-scoped env vars so long-lived tokens never leak through agent output.
github.comrepoAdded 2 Oct 2026, published 9 Aug 2026🧠 AI - Static Analysis Tools & Linters
analysis-tools.dev's source repository is a community-maintained directory of static analysis tools and linters spanning nearly every programming language, tagged for license (proprietary vs open source), maintenance status, and community endorsement. Beyond general code-quality linters, it catalogs many security-relevant static analyzers such as gosec, flawfinder, OWASP Dependency Check, Mariana Trench, Psalm, PHPStan, govulncheck, and WAP, making it a reference point for discovering SAST tooling per language/ecosystem.
github.comrepoAdded 3 Sep 2026, published 9 Aug 2026🛡️ Security - PrimeIntellect-ai/prime-agent
Prime Agent is an open source coding and research agent built on a persistent Python REPL and subagent architecture. Its documentation explicitly warns that it executes model generated code with full user permissions and is not a security sandbox, advising users to only run trusted repositories, instructions, and skills.
github.comrepoPublished and added 9 Aug 2026🛡️ Security - SiberKapan
SiberKapan is a Turkey-focused, community-driven open-source threat intelligence platform that aggregates data from FortiGate webhooks, an 11-service honeypot (HoneypotKapan), nginx/Fail2ban log watchers, and external feeds, publishing it as STIX 2.1/TAXII 2.1, a MISP default feed, Sigma/Suricata/Wazuh exports, and REST blocklists. It also runs a real-time phishing/domain-squatting detector via Certificate Transparency log monitoring with fuzzy typosquat and Punycode/IDN decoding, and safely fingerprints SSH-honeypot malware downloads with SSRF-protected, never-executed hashing enriched via MalwareBazaar. The write-up details concrete anti-abuse safeguards: time-based IP score decay, CDN/cloud-proxy allowlisting, UDP-spoofing exclusion, RFC1918 rejection, and manual review gating for weak phishing signals.
github.comrepoPublished and added 8 Aug 2026🛡️ Security - aurscan
aurscan is a Go-based CLI that hooks into yay/paru to scan a downloaded AUR package's PKGBUILD, .install scriptlets, .SRCINFO and helper scripts before makepkg runs, blocking the build if it looks malicious. It combines offline, quote-aware static rules covering known AUR campaign signatures such as disguised source patch URLs, install-scriptlet worms, masqueraded binary file types, and editor auto-exec triggers with an LLM auditor (Claude Code, Codex, Anthropic API, or a local OpenAI-compatible model) that answers a fixed checklist of yes/no behavioral questions, from which aurscan deterministically derives a verdict, severity and confidence, and fails closed when no backend is available. It documents and defends against real incidents including the July 2025 firefox-patch-bin CHAOS RAT vector, the June 2026 Atomic Arch mass orphan-package takeover pulling a Rust stealer and eBPF rootkit, and the August 2026 xsnow dot-install worm that harvested SSH keys and self-propagated across AUR.
github.comrepoPublished and added 8 Aug 2026🛡️ Security - miqdadbadjuber/anti-slop
anti-slop (antislop) is a rulebook packaged as agent skills that stops AI coding agents from shipping generic UI, filler copy, and formulaic 'AI-shaped' code, without prescribing colors, fonts, or layout. It defines 38 mandatory rules across three tiers (Hard Gate, Purpose-Gate, Quality Locks), a 'Liveliness Toolkit' of ENERGY/RHYTHM/MOTION dials plus a Design Read, and a PASS/FAIL Delivery Gate report run before work ships, split into six loadable skills. It installs via an npx installer, a plugin marketplace, or the skills.sh directory across a dozen agents including Claude Code, Codex, Cursor, OpenCode, Cline, Amp, Gemini CLI, GitHub Copilot, Antigravity, Hermes, Kimi Code, and Pi.
github.comrepoAdded 30 Sep 2026, published 7 Aug 2026🧠 AI - wanmol/goal-flow
goal-flow (goalflow) is a production-oriented framework built on LangGraph that offers two complementary ways to build LLM apps: transpiling Dify Studio's drag-and-drop workflow DSL export into a version-controllable, runnable LangGraph Python file, and building ReAct/Deep/custom agent loops with a vendored agent_kit SDK. It includes a FastAPI HTTP layer, a node library (LLM, code, HTTP, if/else, classifier, iteration, loop, tool, agent, doc-extractor), a chunk-processor that turns raw LangGraph streams into semantic SSE events consumable by pluggable data adapters (Dify/OpenAI/custom), Redis/MySQL persistence, human-in-the-loop interrupts, a skills engine, and Langfuse tracing. It was extracted from an internal production system and reports sustaining 100 concurrent conversations on modest hardware (2 vCPU/4GB per replica).
github.comrepoAdded 30 Sep 2026, published 6 Aug 2026🧠 AI - eternityspring/shuohao-skills
shuohao-skills is a set of five chained Claude Code / Codex agent skills that turn a novel into short-drama production assets: novel-outline (adaptation outline), novel-characters (cast bible), novel-art (scene/prop art bible), novel-script (episode scripts with a duration gauge), and novel-storyboard (shot-by-shot storyboards with actual generated shot images and prompts), plus a standalone character-refs skill that generates character reference images (anchor via GPT, rest via Qwen). Each skill is a self-contained directory with a required SKILL.md and a dependency-free scripts/selftest.mjs, installable via a symlink script that auto-detects Claude Code vs codex, and there is a separate report.mjs assembler that merges the five bilingual HTML reports into one navigable page without touching each skill's own render code (handling CSS/JS scoping and image-path rewriting).
github.comrepoAdded 30 Sep 2026, published 6 Aug 2026🧠 AI - manyuegong33/r0crawl_skills
r0crawl_skills is a Chinese-language skill library for Codex-style AI coding agents, organized as a router plus 196 specialized modules covering web reverse engineering, Android unpacking, Frida instrumentation, native binary analysis, protocol reconstruction, malware triage, firmware analysis and CTF workflows. Rather than dumping advanced terminology at once, it starts novices with four framing questions (what to analyze, what action matters most, what materials exist, what outcome is wanted) and routes them to deeper workflows via lightweight Python scripts (init_case.py, module_router.py, hash_artifact.py) and ten sanitized example playbooks. It's installed by copying the directory into Codex's skills folder, making it a practical illustration of the "router + many domain modules" pattern for packaging large skill collections for coding agents.
github.comrepoAdded 30 Sep 2026, published 6 Aug 2026🧠 AI - manyuegong33/r0crawl_skills
r0crawl_skills is a beginner-friendly Chinese-language skill library of 196 specialized reverse-engineering modules for Codex-style AI coding agents, with a router that asks scoping questions and directs the agent to the right workflow (web RE, Android unpacking, Frida instrumentation, native binary analysis, protocol reconstruction, malware triage, firmware analysis, CTF). It ships lightweight scripts (case init, module router, artifact hashing) and ten sanitized example playbooks covering DEX dump verification, WebCrypto hooking, native loader tracing, PCAP reconstruction, and selective emulation, plus dedicated modules for CAPTCHA/WAF/anti-bot systems, mini-programs, hybrid apps (Flutter/React Native/Electron), and IDA/Ghidra/Rizin automation.
github.comrepoAdded 30 Sep 2026, published 6 Aug 2026🛡️ Security - autoguardrails
autoguardrails is an open-source alignment research scaffold from Santander AI Lab, inspired by Karpathy's autoresearch pattern, that searches over a single mutable policy.md file to minimize attack success rate (ASR) against a fixed jailbreak/obfuscation eval suite while enforcing a benign-pass floor so the guardrail can't just refuse everything. It reports asr_unguarded, asr_with_policy, and policy_delta to isolate the guardrail's contribution from the target model's native safety, and supports both an offline deterministic stub and real OpenAI-compatible target/judge models.
github.comrepoPublished and added 5 Aug 2026🛡️ Security - Dark-Moon
DarkMoon is a self-hosted, GPLv3 AI penetration testing platform that orchestrates 50 specialist agents over an MCP-gated toolbox (Nuclei, BloodHound, sqlmap, Impacket, Naabu, httpx, ffuf, etc.) to autonomously run recon-to-exploitation across web, API, Active Directory, Kubernetes, multi-cloud, CI/CD, databases, IoT firmware, and AI/LLM inference endpoints. It uses a Privacy Gateway that tokenizes real IPs/hosts/credentials into placeholders so raw infrastructure data never reaches the (optionally local, e.g. Ollama/llama.cpp) LLM, and can generate sandbox-validated, exploit-retested pull requests for findings. It also ships a dedicated LLM agent that probes OpenAI-compatible/Ollama/vLLM/TGI inference endpoints for the OWASP LLM Top 10 (prompt injection, jailbreaks, system-prompt leakage) using garak-backed probes.
github.comrepoPublished and added 5 Aug 2026🛡️ Security - SecureAI-Scan
SecureAI-Scan is an offline CLI that performs import-resolved dataflow analysis on TypeScript, JavaScript, and Python code to find LLM/MCP/Agent-Skill/RAG-specific risks (prompt injection, tool poisoning, unsafe output handling, vector-store access control), mapped to the OWASP Top 10 for LLM Applications, Agentic Applications, and MCP Top 10. It distinguishes proven dataflow traces from heuristic keyword matches, scans .mcp.json/claude_desktop_config.json/SKILL.md for tool-poisoning and command-injection patterns (citing the WhatsApp MCP rug-pull and postmark-mcp backdoor), and includes evasion-resistant deobfuscation checks built in response to the "Cloak and Detonate" adversarial study (arXiv:2607.02357) that bypassed most published skill scanners. It also runs offline advisory checks against known-malicious/vulnerable packages (validated against CVE-2025-6514 and CVE-2024-34359) and integrates via GitHub Actions, pre-commit hooks, SARIF output, and an MCP server for Claude Code.
github.comrepoPublished and added 5 Aug 2026🛡️ Security - TRONSEC
TRONSEC is an open-source, browser-based security workbench for the TRON blockchain (TRX mainnet) that lets users inspect wallet addresses, TRC-20 token approvals, smart contracts, transaction calldata, and URLs for risk without connecting a wallet or holding custody. It bundles a wallet risk scanner, AML/sanctions-exposure heuristics, an unlimited-approval monitor, a contract-privilege/proxy checker, a transaction decoder that flags drain patterns, a phishing/typosquat URL checker, and a local in-browser vanity address generator. Production API keys for TronGrid, TronScan, and VirusTotal are kept server-side via a Cloudflare Worker proxy rather than shipped in client JS.
github.comrepoPublished and added 5 Aug 2026🛡️ Security - CyberSec-Blogs
CyberSec-Blogs is a GitHub-hosted, categorized directory of independent cybersecurity blogs run by practitioners, organized into Red Team (54 entries), Threat Hunting (6), Threat Intelligence, Purple Team, and Detection Engineering sections. The list favors personal blogs publishing original research, tradecraft, and tooling over corporate/vendor content, and is community-maintained via PRs/issues under a CC0 license.
github.comrepoPublished and added 5 Aug 2026🛡️ Security - Awesome Android Reverse Engineering
A curated GitHub list covering the full Android reverse engineering toolchain: decompilers (JADX, Apktool, Ghidra, IDA Pro), dynamic instrumentation (Frida, Objection, FriDump, jnitrace), deobfuscation tools (Simplify, Obfu[DE]scate, deoptfuscator), network interception (Burp Suite, MITMProxy, SSLsplit), anti-tamper/root-detection bypass tooling, and malware analysis frameworks (MobSF, Quark Engine, Cuckoo Droid). It also links training courses (Maddie Stone's RE training, Azeria Labs ARM assembly), books (Android Hacker's Handbook, Android Security Internals), and CTF/practice targets (UnCrackable Mobile Apps, KGB Messenger, Flare-On).
github.comrepoPublished and added 5 Aug 2026🛡️ Security - npm-scan
npm-scan is a CLI supply-chain security scanner (@lateos/npm-scan) that inspects npm packages and lockfiles for behavioral attack patterns missed by npm audit/Snyk/Socket, including obfuscated payloads, credential stealers, eBPF kernel rootkits, memory-level OIDC token extraction, GitHub maintainer-account spoofing, and AI-platform-targeted key theft. It ships 23 detectors (D1-D25), validated against real campaigns like IronWorm and Miasma, and outputs SBOM (CycloneDX/SPDX) and SARIF for GitHub Security, plus a workflow to submit critical findings to CISA's VINCE with mandatory manual review. It's free (MIT) for individuals/OSS/evaluation, with paid commercial tiers ($799-$9,900/yr).
github.comrepoPublished and added 5 Aug 2026🛡️ Security - Frieren DAST-AI
Frieren DAST-AI is an open-source dynamic application security testing tool combining an HTTPS MITM proxy with a real-time dashboard and LLM-driven multi-agent active scanner. A YAML-based passive rule engine (62 rules covering headers, cookies, CORS, secrets, error pages, LLM endpoint detection, and Blazor-specific checks) flags issues on every intercepted response, while an LLM planner dispatches parallel VulnAgents (xss, sqli, ssrf, file_read, auth_bypass, secrets, discovery, llm_injection, business_logic, blazor) per endpoint, with an LLM validator confirming findings and adaptive WAF-bypass payload mutation.
github.comrepoPublished and added 5 Aug 2026🛡️ Security - Precogly
Precogly is an open-source, now-OWASP threat modeling platform (React/TypeScript frontend, Django REST Framework/PostgreSQL backend) offering a collaborative DFD editor with trust zones, TM-BOM import/export, and community library packs linked to MITRE ATT&CK, CAPEC, STRIDE, and LINDDUN. It's positioned as compliance-aware, tracing threats and countermeasures to DORA, the EU Cyber Resilience Act, ASVS, NIST CSF, and SOC 2, and exposes a full OpenAPI REST API meant as scaffolding for AI-driven threat modeling assistants.
github.comrepoAdded 3 Sep 2026, published 5 Aug 2026🛡️ Security - autonomous-ai/openharness
OpenHarness (Autonomous) is an open-source command center for running coding agents such as Claude Code, Codex, Cursor, OpenCode, Devin, Amp and Copilot. A native app and per-machine daemon run each agent in its own tmux pane, with a git worktree per harness. Machines are linked by password, with end-to-end encrypted traffic over direct WebRTC, Cloudflare TURN or a keyless relay. It also supports local models (Ollama, MLX-LM, vLLM, Grid) and a Store of domain-specific harnesses (Blender, CircuitJS, MuJoCo, Godogen, Strudel, RDKit, Typst) defined by a harness.json. An optional open-hardware always-on display device shows agent status.
github.comrepoAdded 16 Oct 2026, published 4 Aug 2026🧠 AI - AMAP-ML/LongHorizon-Harness
LongHorizon-Harness (AMAP-ML, package lh-harness) is a Python tool that wraps existing coding/computer-use agents (Claude Code, Codex, OpenCode, DeepSeek Harness) in a durable plan → act → verify → checkpoint/recover loop. It separates Manager, Executor and Auditor roles, accepts only independently verified progress as task state, and restarts rounds from the original goal plus the last verified checkpoint. It supports GUI and terminal workflows via computer-use MCP plugins (codex-computer-use, open-computer-use, clawdcursor), a React/FastAPI web workbench, per-role model and backend selection, and eval suites including Terminal-Bench 2.1; an arXiv paper accompanies it.
github.comrepoAdded 12 Oct 2026, published 4 Aug 2026🧠 AI - Momoko-Ayase/Senbei
Senbei is a Rust-based static unpacker for binaries protected by "CrackProof," working against both Windows PE executables and Android AArch64 shared libraries. It performs a purely static, file-local transformation (no vendor code, no key extraction service) to reverse the protection wrapper for legitimate RE, interoperability, and preservation purposes; one Android packaging variant is unwrapped using an XOR keystream the authors recovered during their own analysis.
github.comrepoAdded 4 Oct 2026, published 3 Aug 2026🛡️ Security - System Prompts Leaks
A community-maintained repository that archives leaked or extracted system prompts — the hidden instructions given to LLM chatbots before user input — captured verbatim from products including Claude/Claude Code, ChatGPT/Codex, Gemini, Grok, Cursor, Copilot, Perplexity, Meta AI, Mistral, DeepSeek, GLM, and others. It serves as a reference corpus for studying system prompt design, extraction techniques, and the system prompt leakage risk class, and is updated regularly as new prompts are exfiltrated from newer model releases.
github.comrepoAdded 3 Sep 2026, published 3 Aug 2026🛡️ Security - asgeirtj/system_prompts_leaks
This GitHub repository collects verbatim leaked/extracted system prompts — the hidden instructions and guardrails — from a wide range of AI products including Claude.ai, Claude Code, ChatGPT, Codex, Gemini, Grok, Perplexity, Microsoft Copilot, Cursor, Meta AI, Mistral, Kimi, DeepSeek, GLM, Qwen and others. It is updated regularly as new prompts are captured, and serves as reference material for AI red-teamers and researchers studying how vendors constrain model behavior and how those constraints can be extracted or bypassed.
github.comrepoPublished and added 3 Aug 2026🛡️ Security - Google Agent Skills
Google's official repository of Agent Skills covering Google products and technologies, including Google Cloud. Skills are installed selectively via `npx skills add google/skills`, and the repo also bundles Google product plugins combining Skills with MCP servers for use in agent harnesses.
github.comrepoAdded 22 Sep 2026, published 3 Aug 2026🧠 AI - patchy631/time-to-first-token
A 10-week, 30-minutes-a-day roadmap (GitHub repo "time-to-first-token") that walks engineers through building one continuously-evolving OpenAI-compatible inference service rather than disconnected tutorials: standing up vLLM and SGLang, reading the PagedAttention/RadixAttention source, instrumenting Grafana dashboards for TTFT/inter-token latency/throughput/queue depth, load-testing past 1000 concurrent requests with GuideLLM, benchmarking FP8/INT4/AWQ quantization and speculative decoding, configuring KV cache eviction, deploying prefill/decode disaggregation on Kubernetes, and building a cost/latency/quality router. It closes with a checklist of common public-benchmark mistakes (sweep request rate, report p50/p95/p99, separate TTFT from inter-token latency, pin versions) and pointers to Stanford CS336, MIT EfficientML.ai, vLLM Office Hours, and GPU MODE for further study.
github.comrepoAdded 2 Oct 2026, published 2 Aug 2026🧠 AI - UseOSINT/Skills
Collection of 28 skill files for coding agents to run OSINT investigations covering domains, emails, usernames, photos, and companies, using techniques like WHOIS, certificate transparency, reverse image search, and breach lookups.
github.comrepoAdded 30 Sep 2026, published 2 Aug 2026🛡️ Security - UseOSINT/Skills
UseOSINT/Skills is a GitHub repo of 28 SKILL.md files that let Cursor, Claude, and other coding agents run open-source-intelligence investigations — 10 end-to-end workflows (e.g. find-anyone, x-ray-a-company, recon-a-domain-passively) built on 18 reusable technique skills (WHOIS, certificate transparency, reverse image search, breach lookups, chronolocation). Each skill ships with reference material (query cookbooks, indicator guides, registry catalogues) and an install script that symlinks the whole set into ~/.cursor/skills, illustrating a chained, workflow-plus-technique pattern for structuring and routing large agent skill libraries. The repo also documents scope/authorization gating and passive-by-default behavior as part of the skill design.
github.comrepoAdded 30 Sep 2026, published 2 Aug 2026🧠 AI - Nomos
Nomos is an open-source permission/authorization layer for custom AI agent tools: agents propose actions (e.g. email.send), and Nomos evaluates them against a policy as ALLOW, DENY, or REQUIRE_APPROVAL before the underlying tool executes. It ships a CLI for writing and running permission tests in CI (with a GitHub Actions example pinning a checksummed release), a Python SDK for wrapping tools with explicit external authorization, and a LangGraph integration that pauses a workflow for human review before resuming execution.
github.comrepoAdded 3 Sep 2026, published 2 Aug 2026🛡️ Security - Kritt-ai/open-kritt
open·kritt is a self-hosted, open-source platform that orchestrates AI coding agents (Codex, Claude Code, or Grok Build) in parallel to hunt for vulnerabilities in remote or local repositories and their dependencies. It breaks security research into small chained prompt "workflows," runs jobs in disposable root-access Docker containers with internet access, then de-duplicates and ranks findings, validates them via post-scripts/PoC generation, and exports share-safe finding bundles. It's the open-source distillation of the internal tooling behind the Kritt team's (Blockian) $1.5M+ in bug-bounty payouts.
github.comrepoPublished and added 2 Aug 2026🛡️ Security - openhackai/OpenHack
OpenHack is an open-source, agentic vulnerability scanner CLI that runs a recon -> hunter -> validation -> verification pipeline over a codebase using open-source LLMs. It uses category- and feature-based hunter agents to find candidate vulnerabilities, validator agents to confirm them, and optional Docker-based sandbox plus headless-browser verification to actually exploit findings (e.g. XSS, SQLi, command exec) and confirm them with real HTTP/DOM execution, reporting CVSS-scored findings with fixes.
github.comrepoPublished and added 2 Aug 2026🛡️ Security - QM
QM is an MIT-licensed, self-hosted "multiplayer" agent harness that lets a company deploy a shared coding/ops agent across Slack and a web app, with per-person and per-room isolated sandboxes, memory, keychains, permissions, and crons. Its security model centers on an org-wide posture (Strict pauses every tool call for approval; Auto blocks private-network access and applies optional content screening; Dangerous disables both) layered under a predeclared command policy that hard-denies things like recursive deletes, plus an explicit Isolated/Open sharing posture that governs cross-scope memory and file access with provenance labeling and audit trails. It supports pluggable harnesses (Pi, OpenCode, Codex, Claude Code) behind a common core and documents its threat model and operator assumptions in SECURITY.md.
github.comrepoAdded 3 Sep 2026, published 1 Aug 2026🛡️ Security - Semantica
Semantica is an open-source Python pipeline (pip install semantica) that ingests enterprise data and builds a queryable Context Graph and knowledge graph with deterministic (LLM-optional) reasoning, ontology management (OWL/SHACL/SKOS), and W3C PROV-O provenance for full decision auditability. It ships modules for ingestion (Databricks, Snowflake, SAP, Kafka, Git, etc.), NER/relation/event extraction, conflict detection and deduplication, Rete/Datalog/SPARQL reasoning, bi-temporal graph queries, polyglot graph storage (RDF stores and LPGs like Neo4j/Neptune), and integrations with Agno, CrewAI, LangChain, and MCP.
github.comrepoAdded 22 Sep 2026, published 1 Aug 2026🧠 AI - ops-engineering-skills
ops-engineering-skills is an open-source library of 296 Agent Skills covering DevOps, DevSecOps, cloud, Kubernetes, CI/CD, GitOps, security scanning, SRE, compliance, databases, messaging, service mesh, serverless, internal developer platforms, MLOps and AgentOps. Each skill is written once to the open SKILL.md standard with machine-checkable frontmatter and eight required sections (prerequisites, steps, pitfalls with fixes, worked example), and works natively across Claude Code, GitHub Copilot, OpenAI Codex, Cursor and Gemini CLI without a translation layer. It ships an automated validator, cross-reference integrity checks, a marketplace/plugin structure for Claude Code, and a generic install.sh/npx installer for any Agent-Skills-compliant agent.
github.comrepoAdded 22 Sep 2026, published 1 Aug 2026🧠 AI - Codex Security CLI
@openai/codex-security is a CLI and TypeScript SDK that uses Codex/LLM agents to scan codebases for vulnerabilities, draft repository-specific SECURITY.md policies, deduplicate findings via embedding similarity, and classify severity against a custom rubric. It supports self-hosted deployment via Docker Compose with a findings service (SQLite-backed dashboard) and can run against multiple inference providers including Amazon Bedrock, OpenRouter, and Fireworks in addition to OpenAI.
github.comrepoPublished and added 1 Aug 2026🛡️ Security - Awesome Offensive AI Agentic Landscape
A comprehensively curated landscape document tracking the offensive AI agent space: ranked open-source pentesting/red-team agent projects (e.g. strix, shannon, VulnBot), uncensored offensive LLMs (Qwythos, WhiteRabbitNeo/DeepHat, BaronLLM) versus security-specialized but aligned models (Foundation-Sec, CyberSecQwen), Claude Code Agent Skills and MCP servers wrapping tools like Metasploit and BloodHound, 116 cross-referenced academic papers on pentest/vuln-discovery agents, capability benchmarks (Cybench, NYU CTF Bench, CyberGym), and a fact-checked Top-20 list of commercial AI pentesting vendors. It also covers competitions like the DARPA AI Cyber Challenge and Tencent's Intelligent Penetration Hackathon, positioning itself as a cross-merge of several other awesome-lists in this niche.
github.comrepoPublished and added 1 Aug 2026🛡️ Security - AgentHound
AgentHound is an open-source offensive security framework that, from a single compromised host, collects local credentials and agent configuration, discovers and fingerprints reachable AI services (MCP servers, A2A agents, model gateways, inference servers like Ollama, vector stores, MLOps platforms, notebooks), reuses harvested credentials to verify concrete access, and writes everything to a checkpointed JSON artifact. An optional analysis server (Neo4j/PostgreSQL-backed) turns the artifact into a queryable attack graph with credential-chain, cross-protocol pivot, exfiltration/execution paths, and prompt-injection-related findings (POISONED_INSTRUCTIONS, POISONED_DESCRIPTION, SHADOWS). It supports an active mode (credential reuse, differential reads, reversible mutation with auto-rollback) and a read-only --stealth mode for OPSEC-constrained engagements.
github.comrepoPublished and added 1 Aug 2026🛡️ Security - Anionex/agent-vision-toolkit
agent-vision-toolkit is a set of CLI tools (glance, ground, detect, trace, crop) plus an agent skill that give text-only LLM coding agents such as DeepSeek vision abilities: intent-aware image Q and A, bounding-box grounding, element detection, SVG tracing of icons, long-screenshot OCR, UI restoration, and GUI automation. It also ships an optional transparent local proxy and single-file native plugins for Codex, Claude Code, Pi, Oh My Pi, and OpenCode so pasted images and built-in image tools are transparently routed to a configurable multimodal API such as OpenAI Chat Completions or Anthropic Messages, without extra prompting.
github.comrepoAdded 2 Oct 2026, published 1 Aug 2026🧠 AI - ChipWhisperer
ChipWhisperer is NewAE Technology's open-source hardware security toolchain for side-channel power analysis and fault injection research, comprising capture-board hardware/PCB schematics, USB and FPGA firmware, target device firmware examples, and Python APIs (ChipWhisperer Capture and Analyzer) for acquiring and processing power traces. It's widely used to demonstrate and teach attacks like differential power analysis (DPA) and voltage/clock glitching against embedded targets such as microcontrollers and crypto implementations. The repository is undergoing a git-history cleanup for the 6.0 release, splitting files across companion repos including chipwhisperer-jupyter.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Awesome Flipper Zero
An awesome-list GitHub repo cataloging Flipper Zero resources: Sub-GHz OOK bruteforce generators, BadUSB ducky-script payload collections, NFC/RFID dumps (Amiibo, Tonies, TouchTunes, event bracelets), custom firmware forks (Unleashed, Momentum, RogueMaster) with rolling-code and community-plugin support, plus apps like a PC vulnerability scanner, mouse jiggler, and BLE spam tool. It serves as a curated index for hardware/RF hacking and red-team tooling built around the Flipper Zero platform.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Awesome Embedded & IoT Security
A curated GitHub list of embedded and IoT security resources maintained by Fraunhofer FKIE, covering firmware analysis frameworks (FACT, emba, Firmadyne, Binwalk, Ghidra, Radare2), hardware hacking tools (JTAGULATOR, Bus Pirate, ChipWhisperer, Proxmark3, HackRF), RF/wireless gear (RTL-SDR, LimeSDR, UberTooth), books, academic papers on firmware security and fuzzing, real-world case studies of device hacking (D-Link, Huawei, Xerox printers), and CTF challenges (Rhme, Microcorruption, IoTGoat). It serves as a comprehensive entry point for beginners and experts doing embedded/IoT security analysis and hardware pentesting.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Damn Vulnerable DeFi
Damn Vulnerable DeFi is a Foundry-based Solidity smart contract security playground featuring intentionally vulnerable challenges around flashloans, price oracles, governance, NFTs, DEXs, lending pools, smart contract wallets, timelocks, vaults, meta-transactions, and upgradeability. Each challenge presents a prompt and vulnerable contracts; solvers write a Foundry test exploiting the flaw to drain funds or bypass restrictions, making it a benchmark for both human auditors and automated security tooling.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Slither
Slither, developed by Trail of Bits, is a Python3-based static analysis framework for Solidity and Vyper smart contracts that runs a suite of vulnerability detectors, visualizes contract internals via 'printers', and exposes an API for writing custom analyses using its SlithIR intermediate representation. It integrates into Hardhat/Foundry/Brownie builds and CI (including GitHub code scanning), claims 99.9% parse coverage of public Solidity code and sub-second average analysis time per contract, and ships companion tools like slither-check-upgradeability, slither-prop, and slither-read-storage.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Awesome Malware Analysis
Awesome Malware Analysis is a curated GitHub list aggregating hundreds of tools and resources across the malware analysis lifecycle: honeypots (Cowrie, Dionaea, Conpot), sample repositories (VirusShare, Malshare, theZoo, VX Underground), IOC/threat-intel platforms (MISP, YARA, ThreatCrowd, URLhaus), online sandboxes (VirusTotal, Cuckoo Sandbox, Hybrid Analysis, any.run), static/dynamic RE tools (IDA Pro, Ghidra, Radare2, x64dbg, angr), deobfuscation utilities, network traffic analyzers (Wireshark, Bro, mitmproxy), and memory forensics frameworks (Volatility, Rekall). It also links essential books, blogs, and training material (Practical Malware Analysis, REMnux, FLARE VM) making it a de facto index for the malware analysis community.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - radare2
radare2 (r2) is a free and open-source command-line reverse engineering framework providing disassembly, binary analysis, debugging (local and remote via gdb/windbg), emulation via ESIL, and hex editing/forensics across an enormous range of CPU architectures and executable file formats (ELF, PE, Mach-O, DEX, WASM, etc.). It is extensible via r2pipe scripting and the r2pm package manager, with a large plugin ecosystem including r2ghidra (decompiler), r2frida (dynamic instrumentation), r2yara, radius2 (symbolic execution), and r2dec.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Ghidra
Ghidra is a free, open-source software reverse engineering (SRE) framework developed by the NSA, offering disassembly, decompilation, graphing, and scripting across Windows, macOS, and Linux. It supports a wide range of processor architectures and executable formats, can run interactively or in automated/headless mode, and allows extension development via Java or Python (including the bundled PyGhidra). It is one of the primary open-source alternatives to IDA Pro for malware analysis and vulnerability research.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - xiazhi88/Desic-Terminal
Desic Terminal is an open-source (MIT) Windows/macOS desktop app for OKX USDT perpetuals trading that bundles an AI trading assistant, AI-gated automated trading, and Python strategy backtesting on a shared real-time state and audit trail. Its notable AI-architecture contribution is a layered permission model where code, not prompts, decides what the agent can do: an AI Sidecar exposes only a scoped, often read-only tool set (e.g. radar.* tools reading a local SQLite market snapshot), delegated sub-agents are always read-only, risk-increasing actions fail closed on uncertain results, and executions use idempotent keys reconciled against exchange state before any retry. It also supports delegating requests to local Codex CLI or Claude Code instead of a hosted model API key, and ships a separate companion MCP server ("Desic OKX Agent") for giving coding agents direct OKX market/account/trading tool access.
github.comrepoAdded 8 Oct 2026, published 31 Jul 2026🧠 AI - thewhiteh4t/FinalRecon
FinalRecon is a Python-based OSINT/reconnaissance tool for web targets, gathering header info, whois data, SSL certificate details, crawling, DNS enumeration, subdomain discovery, port scanning, and directory search in a single utility. It's commonly used during the recon phase of web application pentests to consolidate multiple footprinting techniques into one CLI tool.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - genspark-ai/genoffice
GenOffice is an open-source (Apache-2.0) desktop office suite for macOS/Windows/Linux that opens native .docx/.xlsx/.pptx/PDF/Markdown/HTML files and puts an AI agent inside the editor, applying edits as byte-preserving diffs, tracked changes and live spreadsheet formulas rather than pasted text. It exposes the same engines to coding agents via a `genoffice` CLI, a bundled skill for Claude Code, Codex, Cursor, Gemini CLI, GitHub Copilot, OpenCode and Windsurf, and an MCP server with 29 tools (plus an HTTP variant for headless/remote use), and includes a local SQLite full-text file search optionally reranked by TypeSafe's Jev judgment model. Users can bring their own key (Claude, OpenAI, Gemini, DeepSeek, and others) or sign in with Genspark to route model calls through a proxy.
github.comrepoAdded 30 Sep 2026, published 31 Jul 2026🧠 AI - Beetle
Beetle is an offline-first mobile application security platform that statically analyzes Android APKs and iOS IPAs (including Flutter and React Native apps), combining decompilation, taint analysis, secret/endpoint extraction, certificate and native-binary hardening checks, and CVE enrichment with explainable 'intelligence engines' (ownership, confidence, evidence selection, finding fusion) that correlate findings into evidence-backed attack chains. It maps results to OWASP MASVS/Mobile Top 10, provides source-level navigation, and exports SARIF, CycloneDX SBOM, and PDF reports, with optional (non-scanning) AI assistance via Claude, OpenAI, Gemini, DeepSeek, or local Ollama for explaining findings.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Dark Web OSINT Tools
A curated GitHub list of tools for dark web OSINT and investigation, including onion search engines (Ahmia, OnionSearch, Darkdump, Onion Search Engine), crawlers/scanners (TorBot, TorCrawl, OnionScan, Onioff, Onion-nmap), CTI feed aggregators (DeepDarkCTI), and directories like The Hidden Wiki. Also links the author's own Robin tool and IACA's dark web investigation support resources, making it a one-stop reference for researchers and investigators scoping Tor hidden services.
github.comrepoAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security - Flowsint - OSINT Framework
Flowsint is an open-source, self-hosted OSINT investigation platform that lets analysts visually explore relationships between entities (domains, IPs, ASNs, individuals, organizations, crypto wallets, emails, phones) via a graph interface backed by automated enrichers. It integrates recon modules like reverse/forward DNS resolution, WHOIS, subdomain discovery, ASN/CIDR mapping, breach-database checks, Maigret username search, and crypto wallet transaction/NFT lookups, storing all data locally for investigation privacy. The deployment docs also cover hardening steps for network exposure, including rotating AUTH_SECRET and MASTER_VAULT_KEY, binding backend services (PostgreSQL, Redis, Neo4j, API) to localhost, and a host-header allowlist to defend against DNS rebinding.
github.comrepoAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security - Clairvoyance
Clairvoyance is a Python tool that reconstructs a GraphQL API's schema even when introspection is disabled (e.g., Apollo Server in production mode) by brute-forcing field and type names against the API using wordlists. Output is JSON schema compatible with downstream tools like GraphQL Voyager, InQL, and graphql-path-enum, making it useful for API reconnaissance during bug bounty and pentest engagements.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - hackingtool
hackingtool is a console launcher that bundles 215 curated security tools across 21 categories (recon, OSINT, wireless, phishing, forensics, post-exploitation) so users can install and run them without hunting down individual Git repos. Its newer AI layer maps plain-English goals to the right tool and exact command, plans multi-step objectives with confirmation gates, and drafts engagement reports, while emphasizing safe installs (pinned/SHA-256-verified downloads, no curl|bash, list-form subprocess calls, signed releases with SBOM) and refusing out-of-scope asks like DoS or mass-targeting. It also ships a non-interactive orchestrator (`--engagement`/`--pipeline`) that normalizes tool output into findings.json for red team, blue team, OSINT, bug bounty, and DFIR workflows.
github.comrepoAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security - Hetty
Hetty is an open-source HTTP toolkit for security research written to be a free alternative to Burp Suite Pro, aimed at infosec and bug bounty practitioners. It provides a machine-in-the-middle HTTP proxy with searchable logs, a manual HTTP client for crafting/editing/replaying requests, request/response interception for manual review, project-based scoping, and a web-based admin UI backed by a GraphQL API, distributed via Homebrew, Scoop, Snap, and Docker.
github.comrepoAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security - Talaria
Talaria is a single-binary, pure-Go Linux privilege escalation scanner that enumerates misconfigurations (SUID/SGID, sudoers, capabilities, cron, Polkit JS rules, systemd EnvironmentFile overrides) and links them into confirmed multi-stage root-escalation chains using an embedded Dijkstra pathfinder. It runs read-only with no disk writes, executes in milliseconds, detects backport-aware 2026 Linux kernel vulnerabilities (Dirty Frag, Fragnesia, Copy Fail, DirtyClone, CIFSwitch, PinTheft, pedit COW), and exports JSON/SARIF for SIEM and GitHub Code Scanning integration.
github.comrepoAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security - Mimikatz Missing Manual
A deep-dive, self-paced manual on Mimikatz and Windows identity internals by Carlos Perez (DarkOperator), refined with input from Benjamin Delpy (Mimikatz's author). It covers LSASS credential dumping, Kerberos ticket forgery/roasting/delegation abuse, PKI/smart card and certificate abuse, DCSync/DCShadow domain persistence, and DPAPI secrets, alongside blue team detection strategies and event log signatures.
github.comrepoAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security - vigneshwaran1702/Cloud-Security-Scanner
CSPM tool auditing AWS, Azure, GCP for misconfigurations with AI remediation and compliance mapping.
github.comrepoAdded 30 Sep 2026, published 31 Jul 2026🛡️ Security - lockfale/OSINT-Framework
OSINT Framework is a curated, categorized index of free (mostly) open-source intelligence tools and resources, organized by data type (username, domain, IP, email, social media, etc.) and rendered as an interactive tree at osintframework.com. Each entry in the underlying arf.json is tagged with metadata like whether it requires local install (T), a Google dork (D), registration (R), or manual URL editing (M), plus richer fields such as input/output type, pricing, and opsec notes. It's a long-standing community reference for recon and investigation tradecraft across infosec and other fields.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Sherlock
Sherlock is a command-line OSINT tool that checks over 400 social networks for the existence of a given username, outputting results to text, CSV, or XLSX files. It supports proxying, JSON-based site definitions, NSFW site inclusion, and browsing found accounts directly, making it a staple recon tool for investigators, red teamers, and social engineering research.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - OpenOSINT
OpenOSINT is a Python OSINT agent that wraps 20 investigation tools (holehe for email enumeration, sherlock for username lookup, sublist3r for subdomain enumeration, phoneinfoga for phone intel, plus HaveIBeenPwned, Shodan, VirusTotal, Censys, AbuseIPDB, IP2Location, DNS/SPF/DMARC checks, GitHub, and Bright Data-powered dorking/scraping) behind a natural-language AI interface that issues deterministic tool calls so findings can't be hallucinated. It ships as a REPL, CLI, MCP server (usable from Claude Code/Desktop, Cursor, Windsurf), or browser web UI, with an optional additive FollowTheMoney entity graph for correlating findings and pivoting between investigation results, plus documented reverse-proxy/credential-handling behavior for remote deployments.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - awesome-osint-arsenal
An awesome-list repo that claims 753+ OSINT and security tools across 50 categories. Sections cover username, email, phone, domain/IP, geolocation, image, breach-search, dark web, web scanning and password-cracking tools, plus red team, blue team, DFIR, hardware and training sections. It ships multi-distro installer scripts (install.sh, osint.sh, redteam.sh, blueteam.sh, forensics.sh, hardware.sh, labs.sh, termux.sh) for Kali, Debian and Ubuntu, with partial Arch/Fedora support and a Termux subset. It also gives short usage walkthroughs such as a subfinder + amass + httpx recon chain. Some entries are dual-use (people search, face recognition, phone exploitation, IP camera dorking), and the README says the repo is for authorized research only.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Semgrep Rules (0xdea)
A "battle-tested" collection of Semgrep rules by researcher 0xdea aimed at C (and some C++) vulnerability hunting, covering buffer overflows, use-after-free/double-free, format string bugs, integer truncation/wraparound, command injection, insecure APIs (gets, strcpy, sprintf, scanf family), privilege management ordering, ReDoS, and dozens of other memory-safety and secure-coding checks. Rules are published to the Semgrep registry as "p/0xdea" and can be run directly via `semgrep --config "p/0xdea"` or cloned locally, with SARIF output support for triage in VS Code via SARIF Explorer. The repo also documents a roadmap including porting rules to the Semgrep Pro engine for taint/inter-procedural analysis.
github.comrepoAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security - Web3 Security Tools Hub
A curated GitHub repo cataloging AI tools for smart-contract security auditing, split into free/open-source and paid/closed-source categories and organized by chain/language: Solidity/EVM, Rust/Solana, Move/Sui, ZK/Circom, and multi-language tools. Maintained by pashov, it's meant as a directory for finding AI-assisted auditing tooling rather than a single tool itself.
github.comrepoAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security - hahwul/WebHackersWeapons
WebHackersWeapons is a GitHub-hosted, community-curated list of tools commonly used by web hackers and bug bounty hunters. As an 'awesome list' style repo it aggregates recon, scanning, exploitation, and other web-hacking utilities in one place for practitioners to discover and adopt.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - elementalsouls/Claude-OSINT
Claude-OSINT is a library of 8 drop-in Claude Skills (SKILL.md files, ~10,000 lines) that turn Claude/Claude Code into a structured external-recon operator for authorized red-team and bug-bounty engagements. The core pair (osint-methodology, offensive-osint) covers a 6-stage recon pipeline, an 80-pattern secret scanner, 80+ dorks, and read-only credential validators, while six organization-grade skills add legal-entity-to-footprint mapping, SPF/email-spoofability analysis, FAIR-based dollar risk scoring, continuous exposure re-scan/diff monitoring, cloud/SaaS and dependency-confusion checks, and identity-provider tenant/user-enumeration with explicit hard scope boundaries (no password spraying, no active exploitation).
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Pan-Chera/Multi-Agent-CAD
Multi-Agent CAD (MAC) is a LangGraph-orchestrated multi-agent system that turns natural-language design briefs into editable engineering geometry (STEP/STL/GLB), decomposing mechanisms into separately generated, mated, and QA-validated parts and exporting URDF for robotics/physics simulation. It extends an earlier single-part Text-to-CAD workflow (~1,000 GitHub stars) with visual verification, an independent Judge agent, and an experimental assembly pipeline, reporting on a 10-prompt/141-feature benchmark that it matches a reproduced "CAD Skills" baseline's pass rate (140/141) while using tens-of-times fewer tokens and lower cost under Qwen-based configurations.
github.comrepoAdded 30 Sep 2026, published 30 Jul 2026🧠 AI - deepbeepmeep/Wan2GP
WanGP (Wan2GP) is an open-source 'super app' that packages dozens of open generative video, image, audio and TTS models (Wan, MiniMax H3, LTX-2, Qwen Image, Krea 2, SeedVR2, etc.) behind a single web UI, optimized to run on as little as 6GB VRAM including older Nvidia and AMD GPUs. It bundles LoRA support, quantized checkpoint formats (int8, fp8, GGUF, NVFP4), an agentic assistant ('Deepy') for orchestrating generation jobs, a plugin system, and a headless/API mode for batch and programmatic use.
github.comrepoAdded 22 Sep 2026, published 30 Jul 2026🧠 AI - ThorOdinson246/whatisit-nl2sh
whatisit is a CLI that turns plain-English requests into shell commands using a 941 MB Q4_K_M GGUF model (LoRA fine-tune of Qwen2.5-Coder-1.5B-Instruct) served locally via llama.cpp on CPU. It can optionally use any OpenAI-compatible endpoint. It includes a denylist safety checker (DANGER/CAUTION) with 477 regression cases. On the 300-task InterCode-ALFA benchmark (NL2SH, NAACL 2025) the fine-tune scores 0.620 vs 0.540 for the base (McNemar p=0.004), roughly equal to the untuned 7B and about 11 points behind GPT-4o. A 3B variant is also available, and the author documents the training recipe, data mix and limits.
github.comrepoAdded 16 Oct 2026, published 29 Jul 2026🧠 AI - PentesterFlow/agent
PentesterFlow is an open-source terminal AI agent for authorized offensive-security engagements, connecting to local or hosted LLMs (Ollama, LM Studio, Anthropic, Gemini, DeepSeek, Groq, OpenRouter, etc.) to plan and execute recon, enumeration, vulnerability validation, and evidence-backed reporting against a scoped target. It gates sensitive actions behind analyst approval, bridges with Burp Suite for traffic capture/finding import via a local listener and companion MCP server, and maintains persistent project/personal memory (redacting secrets) to carry lessons and coverage state across sessions. The demo walks through discovering and confirming an IDOR on an orders API and writing findings to a local markdown report.
github.comrepoPublished and added 29 Jul 2026🛡️ Security - redhat-et/ripwire
Ripwire is an offline, single-binary CLI (with optional MCP server) that indexes a repository to give coding agents a ranked, deterministic call graph, task-oriented context bundles (--for, --pack-task), and edit-time checks (--edit-check, --quality-delta, --test-gate) that flag blast radius, contract breakage, and code-quality regressions. It installs skills for Claude Code, Codex, Cursor, Windsurf, Gemini, opencode and aider, and ships extensive self-published benchmarks (docs/EVALS.md, LocBench-style head-to-head comparisons against graph-database MCP servers like codebase-memory-mcp, repowise, graphify and aider) claiming large token and latency savings plus higher file@10 retrieval accuracy. The README includes a detailed field report on using it across a ~20-agent, ~1,500-file C++/Metal orchestration engagement.
github.comrepoAdded 2 Oct 2026, published 29 Jul 2026🧠 AI - Bug Bounty Directory & MCP API
bug-bounties is a community-maintained directory of over 3,000 active bug bounty programs and vulnerability disclosure policies (VDPs), exposed via a public API and a Model Context Protocol (MCP) server. It lets researchers programmatically query scope, rewards, and program metadata, and lets AI coding agents like Claude Code look up bug bounty targets directly.
github.comrepoAdded 3 Sep 2026, published 29 Jul 2026🛡️ Security - RamanMG/Burp-MCP-Unrestricted
An unofficial fork of PortSwigger's Burp Suite MCP server extension that removes the human-approval prompts before an AI client can send HTTP requests or read captured proxy data, and adds tooling aimed at long unsupervised engagements: newest-first proxy history, site map access, scan/crawl driving, and Repeater automation via direct Swing UI manipulation. It also removes the upstream 5000-character response truncation (configurable via maxLength) that could otherwise hide large findings like stack traces or GraphQL introspection dumps from an agent.
github.comrepoPublished and added 29 Jul 2026🛡️ Security - glsec
glsec is a security linter for GitLab CI (.gitlab-ci.yml) configuration files, analogous to zizmor/actionlint for GitHub Actions. It detects misconfigurations like mutable image tags, unquoted user-controlled CI variables in scripts, and other issues mapped to 84 rules across 8 OWASP CI/CD Security categories (excluding IAM and logging, which require platform-level access). It supports baseline/ignore workflows, ShellCheck integration, SARIF/Code Climate/JUnit output for GitLab dashboards, a pre-commit hook, and a Claude Code plugin, and ships releases with Sigstore/cosign signing and SLSA provenance attestations.
github.comrepoPublished and added 29 Jul 2026🛡️ Security - Recon-Skills
Recon-Skills is a curated collection of SKILL.md playbooks for external web security assessments, organized into auth (SSO/OAuth/SAML/MFA), chains (multi-step attack-path analysis), infra, recon (subdomain/DNS/port/tech discovery, route/parameter/API mapping), and redteam (vulnerability-class and platform-specific validation) categories. Each skill documents prerequisites, procedure, pitfalls, and verification criteria, and the skills are designed to be followed manually or loaded as task context by an automation system for authorized penetration testing engagements. It includes a validator script (validate_skills.py) and style/contribution guides to maintain a consistent quality baseline across skills.
github.comrepoPublished and added 29 Jul 2026🛡️ Security - Visa Vulnerability Agentic Harness (VVAH)
VVAH is Visa's open-source agentic harness that runs an eleven-stage (S0–S11) LLM pipeline to discover, verify, report, and optionally remediate/validate application vulnerabilities, built on learnings from Anthropic's Project Glasswing. It combines threat-modeled discovery, multi-lens adversarial analysis, interprocedural taint analysis, and a beta live-HTTP "exploit verification" stage (S6) that proves exploitability and supports regression-testing fixes via ev-replay, outputting Markdown and SARIF 2.1.0 findings with CVSS/CWE data.
github.comrepoPublished and added 29 Jul 2026🛡️ Security - YuroGod/VMPStaticUnpacker
VMPStaticUnpacker is a Python tool that statically unpacks VMProtect-protected Windows PE binaries without executing them, supporting both the legacy plaintext PACKER_INFO metadata format and the compact rotating-XOR format seen in VMProtect 3.9.5 PE32+ samples. It recovers the destination key by XORing the encoded destination with the first packed section's RVA and rolling the key with ROL32(key,7), then validates candidate tables and LZMA streams before rebuilding a memory-image PE for static analysis. It does not devirtualize protected code, recover the original entry point, strip the VMProtect runtime, or fix imports.
github.comrepoAdded 2 Oct 2026, published 29 Jul 2026🛡️ Security - DevCop95/shodan_reconsx
recons101x (shodan_reconsx) is a passive-by-default Python CLI that enumerates hostnames published to certificate transparency logs via ctl.shodan.io, requiring no Shodan API key. It supports optional active features — DNS resolution, TCP/HTTP reachability probing on ports 443/80, bounded live scans, and certificate metadata enrichment — with status states (DNS_ONLY, TCP_REACHABLE, HTTP_REACHABLE, STALE), JSON/TXT output, and safeguards like --max-time, --active-only, and explicit warnings to only scan authorized domains.
github.comrepoAdded 30 Sep 2026, published 29 Jul 2026🛡️ Security - 1N3/Sn1per
Sn1per is an open-source Community Edition offensive-security platform that automates reconnaissance, vulnerability scanning, and exploitation by orchestrating 90+ third-party tools such as Nmap, Metasploit, Burp Suite, and Nessus into unified scan modes (normal, stealth, discover, airstrike, nuke). It ships with 600+ exploits and 10,000+ detections, supports Docker deployment, workspace-based loot management, and scheduled scans for external attack surface management. Paid Professional and Enterprise tiers add a web UI, reporting exports, and a JSON API on top of the same source-available CLI scanning engine.
github.comrepoPublished and added 26 Jul 2026🛡️ Security - Bug Bounty Lab101
Bug Bounty Lab101 is a workspace that structures the real HackerOne bug bounty workflow: document program scope, run scope-gated recon/vuln scanning via bugbounty-hunter.sh (backed by a 400+ tool arsenal spanning recon, DNS enumeration, web scanning, exploitation, and cloud/subdomain-takeover checks), then produce a triage-ready H1 report with Hacktivity dedup checks. It also integrates T3MP3ST, a separate multi-agent offensive framework that connects local AI coding agents (Claude Code, Codex) to automate target investigation, and ships a legacy-vm-practice lab (DVWA/Metasploitable-style) for safe skill-building outside real program scope.
github.comrepoPublished and added 25 Jul 2026🛡️ Security - Dalfox
Dalfox is an open-source XSS scanning and parameter analysis tool, rewritten in Rust for v3 (previously Go, preserved on the v2 branch). It automates discovery via parameter mining and static/BAV analysis, detects reflected, stored, and DOM-based XSS with DOM/AST verification, and includes WAF fingerprinting with confidence scoring and bypass tracking, plus a REST API and MCP stdio server for extensibility.
github.comrepoPublished and added 25 Jul 2026🛡️ Security - ShortDot Zone Abuse Evidence
PhishDestroy's shortdot-evidence is a daily-updated GitHub investigation into ShortDot SA, the Luxembourg registry operator behind the .icu, .bond, .cyou, .sbs, .cfd, .buzz and .qpon gTLDs, documenting that 51,985+ tracked domains impersonate brands like Chase, Binance, MetaMask and Ledger and that ~70% of registered domains in these zones carry no DNS records (metric-padding rather than legitimate use). It publishes machine-generated IOC/blocklist files and analytics built from a per-TLD zone-file pull cross-referenced against Spamhaus DBL, SURBL, OpenPhish, URLhaus, PhishTank and AlienVault OTX, and ties the zones to concrete criminal cases (FBI's LabHost domain list, Google v. DOES/Yucheng Chang RICO suits, the Revolver Rabbit XLoader/Formbook C2 campaign using 500k+ .bond domains). It also details structural conflicts of interest between ShortDot, its registry infrastructure provider Team Internet Group/CentralNic, registrar partner NameSilo, and the brand-protection vendor NameBlock, backed by Interisle Consulting Group phishing-volume statistics.
github.comrepoPublished and added 25 Jul 2026🛡️ Security - Birfy/agentdescent
agentdescent is a Python framework that treats self-improving agents as an optimization problem: N workers propose diffs (edits) to a shared skill/prompt/harness artifact in parallel, and a barrier-free aggregator merges them via conflict resolution, fusion and statistical acceptance rather than gradient averaging, committing winners to a version-controlled ledger. It ships a single `evolve()` entry point with pluggable strategy, scorer, and proposal functions, an MCP server and CLI for agent-triggered runs, and faithful reimplementations of 20 published self-evolution algorithms (ACE, GEPA, EvoSkill, SkillOpt, ADAS, DGM, OpenEvolve, ERA, PromptBreeder, AFlow, Self-Refine, Reflexion, SICA, Gödel Agent, Voyager, SkillWeaver, Absolute Zero, R-Zero, Agent0, Genesis) that plug into the same engine for apples-to-apples comparison. The accompanying paper (Chen, 2026) gives a closed-form condition for when concurrent edits can merge and reports confidence intervals rather than false-precision p-values.
github.comrepoAdded 30 Sep 2026, published 24 Jul 2026🧠 AI - thomasbuilds/Spectre
Spectre is a free, open-source Android app (min API 31) for observing and interacting with the surrounding wireless environment, combining passive monitoring of Bluetooth LE, Wi-Fi, cellular (2G-5G), and GNSS with a growing set of pentesting tools. Notable features include a BLE GATT inspector that can read/write characteristics on connected devices, a local-network scanner (TCP-connect host discovery, SSDP/UPnP, mDNS/DNS-SD, banner grabbing, reverse DNS), iBeacon broadcast spoofing, and a computed aggregate RF-exposure figure derived by correctly summing per-emitter power in linear watts rather than dBm. It also documents Android platform limitations affecting wireless recon, such as invisible 5G NSA signal, Wi-Fi scan throttling, and single-carrier cell visibility.
github.comrepoPublished and added 23 Jul 2026🛡️ Security - aniqfakhrul/CVE-2026-54121
Certighost is a Python PoC for CVE-2026-54121, an Active Directory Certificate Services attack that spins up rogue SMB/LSA and LDAP listeners to intercept the CA's NetLogon-based identity resolution during certificate enrollment. By impersonating a low-privileged computer account and redirecting the CA's lookups to the target Domain Controller's identity, the tool causes the CA to issue a valid certificate for the DC, then uses PKINIT with that certificate to retrieve the DC's Kerberos TGT/ccache and NT hash — a full domain-compromise chain from a single low-privileged account. The repo includes fixes for an in-the-wild NetLogon trust-account error (STATUS_NOLOGON_SERVER_TRUST_ACCOUNT) and a SAN-spoofing bypass for CAs enforcing ESC6-style EDITF_ATTRIBUTESUBJECTALTNAME2 protections.
github.comrepoAdded 5 Oct 2026, published 23 Jul 2026🛡️ Security - gowitness
gowitness is a Golang website screenshot utility that drives Chrome Headless to capture screenshots of web interfaces at scale from the command line, ingesting targets from URL lists, CIDRs, Nmap, or Nessus results. It can also capture request/console logs, headers, and cookies, writing results to SQLite, JSONL, or CSV, with a bundled web-based report viewer and API for triaging large recon datasets.
github.comrepoAdded 3 Sep 2026, published 23 Jul 2026🛡️ Security - LSPosed/LSPromise
LSPromise is a GitHub repo and detailed writeup documenting a complete Android privilege-escalation exploit chain from an untrusted local app to root/kernel, with no memory corruption required. It chains a logic bug in Telecom's InCallController.java (CVE-2026-49881) that lets arbitrary code run inside system_server, pivots via ActivityManager reflection into com.android.networkstack to reach the DirtyFrag kernel 1-day (CVE-2026-43500/CVE-2026-43284), and then uses a DirtyPipe-style binary-patching technique (crash_dump, modprobe, vendor_file labeled kernel module) to disable SELinux and launch KernelSU with root. Tested on Pixel 10 running Android 17; the first bug was fixed in the September 2026 security bulletin.
github.comrepoAdded 2 Oct 2026, published 23 Jul 2026🛡️ Security - BountyForge
BountyForge is a Claude Code skill that spins up 8 specialized agents in parallel to hunt for vulnerabilities across web/API, smart contracts (EVM, Move, Solana, TRON), infrastructure, and supply-chain targets, then deduplicates and runs findings through a four-gate validation pipeline (Refutation, Reachability, Trigger, Impact) before CVSS-scoring them into submission-ready HackerOne/Bugcrowd/Intigriti/Immunefi reports. It orchestrates local tools (nmap, ffuf, sqlmap, amass, ZAP, Burp Suite) when Claude Code execution is enabled, integrates with a companion `bug-bounty-intelligence-mcp` MCP server for Solidity scanning via "Al-Mizaan v3" 7-gate deep validation, and also offers a paid Firecracker-microVM cloud version at bountyforge.xyz.
github.comrepoPublished and added 22 Jul 2026🛡️ Security - SeClaw
SeClaw is a benchmark framework for evaluating security risks of autonomous LLM agents, combining spec-driven synthesis of security tasks (covering resource, task, environment, and intrinsic-agent risk categories) with execution-based evaluation in a Docker sandbox. The repo ships SeClaw-Bench, a public dataset of 150 OpenClaw task directories, plus batch-execution scripts that record full agent trajectories (tool calls, file ops, outputs) and grade them against a multi-dimensional risk rubric covering information leakage, privilege misuse, content safety, and compliance risks, rather than only judging final responses.
github.comrepoPublished and added 22 Jul 2026🛡️ Security - ClawSecCheck
ClawSecCheck audits OpenClaw agent installs for prompt injection, malicious MCP servers, and supply-chain risk in skills and dependencies.
github.comrepoPublished and added 22 Jul 2026🛡️ Security - HackingLZ/gibson
Gibson is a Rust-based network monitoring toolkit with a lightweight agent, server, and parser that maps process-to-network connections, detects cloud provider ownership (AWS/Azure/GCP/Cloudflare), flags beaconing candidates and EOL OS risk, and auto-generates iptables/Windows firewall rules. It supports AES-256-GCM encrypted uploads, ASN/ARIN-based IP ownership lookups, and SQL/JSON report exports for cross-host threat hunting.
github.comrepoPublished and added 22 Jul 2026🛡️ Security - QoderAI/better-harness
Better Harness is an MIT-licensed plugin/CLI from QoderAI that runs inside a coding agent (Claude Code, Codex, Qoder, Cursor, GitHub Copilot CLI, Qwen Code, Pi, Kimi Code and others) via a /better-harness command. It collects project and session evidence and scores five dimensions of the "Agent Work Loop" (feedforward guides like AGENTS.md, specs and Skills; feedback sensors like linters, tests and Hooks). It outputs HTML/Markdown/Canvas reports with prioritized findings, repair plans and acceptance checks, and keeps missing evidence explicit rather than inventing scores.
github.comrepoAdded 12 Oct 2026, published 21 Jul 2026🧠 AI - yolorouter/yolorouter
Yolorouter is a free, self-hosted, single-binary LLM gateway that translates between the four major chat wire protocols — OpenAI Chat Completions, OpenAI Responses, Anthropic Messages, and Gemini generateContent — so a client built for one provider (e.g. Claude Code) can be pointed at any other. It adds multi-provider failover, round-robin upstream API key pooling with rate-limit/quota handling, per-key budgets and access control, a multi-user admin console with OAuth2/OIDC SSO, and native image/video generation support for OpenAI-shaped and non-OpenAI-shaped providers (DashScope, Volcengine Ark, Kling, MiniMax). It also ships cost-optimization features — deterministic system-prompt injection and tool-output compression for coding agents — backed by a published benchmark, plus built-in usage/cost observability.
github.comrepoAdded 2 Oct 2026, published 21 Jul 2026🧠 AI - Gabson0x/pentdem
pentdem is an autonomous AI-powered pentesting CLI/pipeline that fans out 15+ vulnerability-class hunters (XSS, SQLi, SSRF, IDOR, SSTI, JWT, GraphQL, etc.) and 8 advanced attack skills (mass assignment, race conditions, cloud metadata, OAuth/OIDC, subdomain takeover, credential harvesting) in parallel, using an LLM to adapt strategy mid-scan. It wraps real tools (nmap, sqlmap, nuclei, ffuf, subfinder, httpx) in Docker isolation and adds a novel gate chain — quality gate, kill-chain builder, adversarial cross-model validation (a second model tries to disprove each finding), a capability execution ledger (proves each hunter actually ran instead of silently crashing), and a ship-discipline gate — before mapping surviving findings to MITRE ATT&CK/OWASP Top 10/CVSS and generating reports.
github.comrepoPublished and added 20 Jul 2026🛡️ Security - weirdmachine64/GhidraGPT
GhidraGPT is a Ghidra extension that sends a selected function's decompiled C to an LLM provider (OpenAI, Gemini, Ollama, etc.) and streams results back into a console, offering three actions: Explain (natural-language summary), Rewrite (recovers names/types and writes them back into the Ghidra database), and Audit (best-effort single-function review for issues like unbounded copies and integer overflows). Analysis is scoped to one function's decompiler output with no cross-function dataflow, so audit findings are leads to verify rather than sound static-analysis proof; API keys are stored locally with only XOR obfuscation, not real encryption.
github.comrepoPublished and added 20 Jul 2026🛡️ Security - dinosn/fastjson-jsontype-rce-lab
A dual-track research lab reconstructing Fastjson RCE chains: a legacy JDK 8 direct-remote-class JSONType RCE for Fastjson 1.2.83, and a modern JDK 17 retained-JAR via proc-self-fd composition that works even with AutoType disabled and DTO binding in place, exploiting how ParserConfig.checkAutoType probes every type value via getResourceAsStream. It also reproduces an independent fastjson2 2.0.57/2.0.62 autoType bypass disclosed by Chaitin, where ObjectReaderSeeAlso hardcodes SupportAutoType, letting seeAlso/JsonSubTypes/sealed-type modeling trigger remote class loading even with autoType disabled. The repo ships dependency-free Python scanner tools for passive log detection, static artifact inventory, and safe active reachability probing via Burp Collaborator or interactsh.
github.comrepoAdded 2 Oct 2026, published 20 Jul 2026🛡️ Security - ailinone/collective-intelligence
Collective Intelligence is an open-source (AGPL-3.0) OpenAI-API-compatible gateway that routes a single request across a continuously-discovered pool of AI models (claimed ~90 provider integrations, 103,224 indexed models) using one of 32 coordination strategies - consensus with convergence floors, blind debate, expert panels, devil's-advocate consensus, cost-cascade, best-of-N with objective verification - instead of sending it to one model. Every response carries an ailin_metadata provenance record (strategy used, models used, cost, dissent), and the repo ships a reproducible benchmark harness with raw per-execution CSVs claiming the coordinated pool beats GPT-5.5-pro, Claude Opus 4.8, Gemini 3.1 Pro and Grok 4.3 on verifiable tasks (97% vs 68-82%). It installs via Docker Compose, exposes an OpenAI SDK-compatible base_url swap, and supports a no-API-key Ollama degraded self-hosted mode.
github.comrepoAdded 2 Oct 2026, published 20 Jul 2026🧠 AI - Vincentwei1021/video-shotcraft
video-shotcraft is an installable agent skill for Claude Code and Codex that storyboards, animates, and sound-designs cinematic product promo videos using Remotion, with a library of 157+ shot recipe cards, 214+ motion previews, and a complete production template (Ink Press). It ships a post-delivery "CapCut-style" editing workbench for adjusting shots/captions/SFX and can export finished films as editable JianYing (CapCut CN) drafts, alongside a sibling skill, video-talkcraft, for voice-synced narration videos.
github.comrepoAdded 5 Oct 2026, published 19 Jul 2026🧠 AI - yuezhiai/jonex
Jonex is an open-source enterprise AI knowledge platform that combines multimodal document/video parsing with an ontology-based knowledge compiler, indexing content into both a vector store (Milvus) and a knowledge graph (Neo4j) for source-grounded retrieval. It exposes ontology-first hybrid search APIs with reasoning traces and references, and integrates with LightRAG, RAG-Anything, and MinerU for graph-enhanced retrieval and document parsing, plus an MCP server for tool exposure.
github.comrepoAdded 2 Oct 2026, published 19 Jul 2026🧠 AI - AI Security Briefing
SingGuard-NSFA is an open-source guardrail framework (released as 0.8B/2B/4B/9B model checkpoints) that targets operational threats in LLM agents—prompt injection, sensitive-info extraction, malicious code requests, tool misuse, and resource exhaustion—rather than just content-safety issues. It's built on a CIA-triad-grounded taxonomy of 185 risk variants across 7 domains (cross-validated against OWASP guidelines) and a 133-language benchmark with 93K+ samples, offering both generative chain-of-thought auditing and ~50ms real-time classification heads. It beats Llama Guard 3, WildGuard, and GPT-5.1 by 6-12 F1 points on multilingual benchmarks, and can also be plugged into Llama Guard 3 as a lightweight enhancement (+17.6 F1).
github.comrepoPublished and added 19 Jul 2026🛡️ Security - capitalone/VulnHunter
VulnHunter is Capital One's open-source agentic AI vulnerability scanner built as a set of Claude Code skills (/vulnhunt, /vulnhunter-fix, /vulnhunt-fix-verify) that runs on Claude Opus. Instead of pattern-matching like traditional SAST, it does attacker-first forward analysis from entry points, runs a "falsification engine" to discard unexploitable findings, and generates evidence-backed remediation patches; it also ships a headless agent runtime and a benchmarking harness tested against OWASP NodeGoat, Juice Shop, and WebGoat.
github.comrepoAdded 19 Jul 2026🛡️ Security - Awesome AI Web3 Security
A curated, verified awesome-list of AI-powered tools for smart contract and blockchain security, covering autonomous auditor agents (Hound, Plamen, Aether, SolidityGuard), commercial AI audit platforms (Sherlock AI, Cantina Apex, Zellic V12, Nethermind AuditAgent), MCP-based auditing plugins (Trail of Bits Skills, Claudit, Slither MCP, Solodit MCP Server), real-time on-chain ML monitoring (Forta Network, AnChain.AI), and benchmark/training datasets (EVMbench, SCONE-bench, ScaBench, SmartBugs). Every entry requires a real AI/ML/LLM component plus a specific Web3 security focus, with open-source entries needing 25+ GitHub stars, positioning it as a practical index for the emerging AI-driven smart-contract-audit tooling ecosystem.
github.comrepoAdded 3 Sep 2026, published 18 Jul 2026🛡️ Security - Argo
Argo is an LLM-native static application security testing tool that drives Claude Code, Codex, Gemini, or local models (via Ollama/LM Studio) as an AI analyst to audit source code, extract security invariants, and produce reviewable vulnerability reports with optional patch generation and ASan-verified proof-of-concept crashes. It positions itself as a complement to rule-based SAST tools like CodeQL and Semgrep, targeting logic/authorization bugs that fixed patterns miss, and has been used to find real, disclosed vulnerabilities across 15 audited open-source projects (53 PRs, 2 CVEs). It supports two modes — general code audit and bug-bounty triage with scope-enforced, read-only, opt-in live verification guardrails.
github.comrepoAdded 3 Sep 2026, published 18 Jul 2026🛡️ Security - jit
jit is a macOS (Apple Silicon) tool that moves plaintext secrets from .env files, ~/.aws/credentials, shell exports, .npmrc, and MCP configs into a Touch ID-gated local encrypted vault, leaving decoy files on disk and injecting real values only into the specific process that requests them via execve, native credential-helper protocols (AWS credential_process, docker/git credential helpers), or ephemeral named-pipe (FIFO) mounts. It adds per-process consent prompts naming the requesting tool/agent, time-bounded "process grants" for unattended AI agents (e.g. Claude, Codex) to use credentials overnight, and a durable audit log of every credential read, unlock, and denial. It explicitly targets the risk that AI coding agents and CLIs run with full user permissions and can read plaintext secrets, treating agent MCP configs and wrapped AI CLIs as first-class.
github.comrepoPublished and added 18 Jul 2026🛡️ Security - OpenNVR
OpenNVR is a self-hosted, Docker-deployed network video recorder for ONVIF/RTSP IP cameras that is explicitly designed around a "sovereign, air-gapped by default" security architecture: network isolation between camera/gateway/analytics planes, Fernet-encrypted credentials at rest, RTSPS transport, and two default-deny gates (DEPLOYMENT_MODE=offline, AI_SOVEREIGNTY=local_only) that keep cloud and AI egress returning HTTP 403 until explicitly opened. It's positioned as a response to systemic IP-camera weaknesses (default creds, hard-coded keys, unsigned firmware, vendor cloud aggregation) exploited historically by the Mirai botnet and the 2021 Verkada camera-feed breach, and targets regulated buyers newly barred from Hikvision/Dahua/Uniview/Edimax-class vendors under NDAA §889 and 2025-26 FCC enforcement. Its pluggable AI Adapter Contract (Apache-2.0 SDK) lets third parties add detection/LLM capabilities out-of-tree, with correlation-ID audit trails and SHA-256 model fingerprinting for compliance evidence.
github.comrepoPublished and added 18 Jul 2026🛡️ Security - EVM Hack PoC
A public GitHub repository aggregating proof-of-concept exploit archives for EVM (Ethereum Virtual Machine) smart contract hacks, generated from the companion evm-hack-registry dataset and meant to be consumed by the evm-hack-analyzer tool. It's positioned as raw material for blockchain security research, education, and building automated PoC-analysis tooling rather than a single vulnerability writeup.
github.comrepoAdded 3 Sep 2026, published 18 Jul 2026🛡️ Security - EVM Hack Analyzer
EVM Hack Analyzer is a static, backend-free, in-browser debugger that forks chain state at a historical transaction, replays it in an in-browser EVM (@ethereumjs/vm), pulls verified Solidity sources from Etherscan, and produces a pc-to-source-line map so researchers can step through a real exploit opcode-by-opcode or line-by-line. It supports both native replay of a historical tx hash and loading pre-built scripted exploit ZIPs from the companion evm-hack-poc dataset (mirroring DeFiHackLabs and crypto.training/hacks), letting users annotate the vulnerable line and exploit steps, then export/share a self-contained PoC via ZIP or IPFS. It's aimed at smart-contract vulnerability research and community-sourced exploit PoC archiving, entirely client-side with no server or persistent backend required.
github.comrepoAdded 3 Sep 2026, published 18 Jul 2026🛡️ Security - OSCP & CPTS Study Notes
A GitHub repository (also published as a GitBook) of study notes compiled while pursuing the Hack The Box CPTS certification, structured to double as OSCP prep material. It covers networking fundamentals, enumeration, privilege escalation, Active Directory attacks, and pivoting with hands-on methodologies and tool usage rather than just theory.
github.comrepoAdded 3 Sep 2026, published 18 Jul 2026🛡️ Security - dstours/OctoC2
OctoC2 is a GitHub-native command-and-control framework built with TypeScript/Bun, featuring a beacon, durable controller, operator dashboard, and CLI. It supports multiple encrypted transports (GitHub Issues/branches/Actions/Gists/Git Notes, HTTPS/WebSocket, gRPC with mTLS, GitHub Actions OIDC, and relayed Codespaces SSH tunnels) with a signed task protocol, Ed25519 beacon identities, exclusive delivery leases, and replay-protected state for authorized red-team and security research engagements.
github.comrepoPublished and added 18 Jul 2026🛡️ Security - 0x1ceKing/HTB-Certified-Penetration-Testing-Specialist
A GitHub repository compiling personal study notes and cheatsheets for HackTheBox's CPTS (Certified Penetration Testing Specialist) certification, organized by module: network enumeration (Nmap), web footprinting, file transfers, shells/payloads, Metasploit, password attacks, pivoting/tunnelling, Active Directory enumeration and attacks, web app attacks (SQLi, SQLMap, XSS, LFI, file upload, command injection, Ffuf), and Linux/Windows privilege escalation. It functions as a reference guide mirroring the official HTB Academy course structure rather than original research.
github.comrepoPublished and added 18 Jul 2026🛡️ Security - gioblu/NPC-Forge
NPC-Forge is a framework for building deterministic, non-ML conversational NPCs/agents with multi-turn context, sentiment analysis, and tool-call support, designed to run on CPU even on embedded or obsolete hardware. It ships with an OpenAI-compatible API server so its deterministic agents can be plugged into LLM harnesses like Open WebUI or GitHub Copilot, and includes TERMy, a bundled NPC that transpiles natural-language prompts or scripts into shell commands without using any model. Agents are defined and updated via a dataset format (NDF) rather than trained, with a CLI (npc-forge list/serve/install/reboot) for managing and running them; currently an experimental Linux/WSL-only release under AGPL-3.0.
github.comrepoAdded 30 Sep 2026, published 18 Jul 2026🧠 AI - luqman-v1/9router-go
9router-go is a single-binary Go port of 9Router, an LLM gateway that sits between CLI coding tools (Claude Code, Cursor, Codex, Cline, OpenClaw, Gemini CLI, OpenCode) and 40+ AI providers/100+ models. It adds RTK token compression (claimed 20-40% token savings on tool_result content), tiered auto-fallback (subscription → cheap → free providers), multi-account round-robin, per-key proxy pools, and an embedded Svelte dashboard backed by SQLite, with database compatibility to share state with the original Next.js 9Router. It targets the practical problem of coding-agent subscription quota exhaustion and token cost, not a research contribution.
github.comrepoAdded 7 Oct 2026, published 18 Jul 2026🧠 AI - CyberSunil/LLMVault
LLMVault is a self-hosted, deliberately-vulnerable training range modeled on WebGoat but for LLM applications, covering 25 labs across the OWASP Top 10 for LLM Applications (2025) - prompt injection, jailbreaking, data/model poisoning, agent exploitation, model extraction, and insecure downstream output handling. It ships two modes: a scored Play Mode with scripted assistants for repeatable flag capture, and an unscripted Live Mode that points the same attacks at a real local Ollama model (qwen2.5:3b-instruct) with a freshly minted per-session secret, requiring the player to actually talk the model into leaking it. Each lab pairs the attack with a written defense explanation, and an expert tier is shipped AES/Fernet-encrypted and unlocked manually by the maintainer.
github.comrepoPublished and added 18 Jul 2026🛡️ Security - VulnHunter (Capital One)
VulnHunter is Capital One's open-source agentic AI security scanner, implemented as a set of Claude Code skills (/vulnhunt, /vulnhunter-fix, /vulnhunt-fix-verify) that require Claude Opus. Instead of traditional sink-first SAST pattern matching, it reasons forward from attacker-accessible entry points (APIs, uploads, network messages), runs a 'falsification engine' to discard unexploitable findings, and generates evidence-backed exploit paths and targeted code fixes; it also ships a headless agent for CI/CD-scale scanning and a benchmarking harness against corpora like Juice Shop, WebGoat and NodeGoat.
github.comrepoAdded 22 Sep 2026, published 18 Jul 2026🛡️ Security - GoogleCloudPlatform/k8s-aibom
k8s-aibom is a Kubernetes controller from GoogleCloudPlatform that generates CycloneDX 1.6 ML-BOM documents at runtime for AI workloads — inference services (vLLM, TGI, Triton, Ollama), agent stacks (LangChain, AutoGen, CrewAI), RAG/vector DB infrastructure (Milvus, Qdrant, Weaviate), and training/eval jobs — by watching Kubernetes API objects with no privileged access. Each BOM attribute carries a declared/inferred/unresolved confidence flag and evidence locator, and the project positions its output as auditor-traceable evidence for EU AI Act Article 12/50, NIST AI RMF, and ISO/IEC 42001 compliance, with redaction filters, immutable GCS write-once sinks, and Sigstore-signed release attestations.
github.comrepoPublished and added 18 Jul 2026🛡️ Security - Icex0/wp2shell-poc
wp2shell-poc is an independent proof-of-concept tool for the wp2shell vulnerability chain in WordPress core: an unauthenticated route-confusion bug in the REST /batch/v1 handler (serve_batch_request_v1) that desynchronizes matched-handler and validation arrays when a sub-request fails wp_parse_url(), letting a GET posts item-route request be dispatched under get_items() so the author_exclude parameter reaches WP_Query's author__not_in query var as unsanitized SQL. The tool's check/read/shell commands detect the route-confusion marker pattern, extract data via UNION/error-based/boolean-blind SQLi, and (without credentials) chain UNION fake-post rendering into oEmbed cache post creation, ID recovery via SQLi, and a poisoned batch request that creates a real WordPress administrator account, finishing with a plugin-upload webshell. Affects WordPress builds before 7.0.2 (or 6.9.5 on the 6.9 branch); links out to Searchlight Cyber's advisory and Elastic/Eye Security detection guidance.
github.comrepoAdded 2 Oct 2026, published 17 Jul 2026🛡️ Security - drumih/turbo-fieldfare
TurboFieldfare is a custom Swift + Metal inference runtime that runs the instruction-tuned Gemma 4 26B-A4B mixture-of-experts model on Apple Silicon Macs with as little as 8 GB of RAM. Rather than loading the full 14.3 GB model into memory, it keeps a 1.35 GB shared core and FP16 KV cache resident and streams only the per-token routed experts from SSD via a bounded 16-slot LFU expert cache, using 4-bit MLX-style affine quantization and custom Metal kernels for GEMV, attention, MoE, RoPE and sampling. It ships a native Mac app, CLI, and a loopback OpenAI-compatible server with function-tool support, plus an optional vision-tower companion pack for image input on M2+ Macs, and documents 103 benchmarked experiments behind its design choices.
github.comrepoAdded 2 Oct 2026, published 17 Jul 2026🧠 AI - icedracon/adhammer
ADhammer is an open-source Rust CLI for authorized Active Directory assessments that discovers domain state, maps attack paths to Tier-0, and reports findings with an explicit evidence/validation status. Its v1.5.2 release adds an ESC1-based KB5014754 PKINIT bypass against Full-Enforcement KDCs, pass-the-hash DCSync, workstation preflight checks, and a hardened error classifier. It exposes a 74-method catalog spanning enumeration, Kerberos/credential attacks, delegation/S4U abuse, coercion/relay, and remote execution, plus reusable Rust protocol crates and an SDK.
github.comrepoAdded 2 Oct 2026, published 17 Jul 2026🛡️ Security - AI-Powered Threat Modeling
AITM is an open-source Python CLI (MIT licensed) that automates STRIDE threat modeling of system architectures using LLMs via Bedrock, OpenAI, or local Ollama. Given a text description or architecture diagram image, it identifies assets and data flows, generates STRIDE-categorized threats with CWE mapping (e.g. CWE-89 for SQLi), scores risk on a 5-level matrix, and outputs actionable mitigations in Markdown or JSON. The engine is stateless with a Pydantic data contract, designed to later support a REST API and frontend; an enterprise edition with additional features is offered commercially.
github.comrepoAdded 3 Sep 2026, published 17 Jul 2026🛡️ Security - tiwe0/r0dump
r0dump ports the FART active-invocation dumping technique into the Android 16 / ART runtime, hooking DEX registration, class loading and method dispatch directly inside ART to force packed apps to decrypt their code at runtime. It also captures DEX loaded via InMemoryDexClassLoader, reconstructs shifted ID tables back into standard DEX files, and recomputes Adler-32/SHA-1 checksums, with a companion "R0dump Manager" app (including an ADB-driven MCP bridge) for target selection, repair and ZIP export of dumped samples for inspection in JADX/dexdump. The reference build targets a OnePlus 9 running LineageOS 23.2 with test-keys, and the project ships git-format-patch sets for porting to other Android 16 devices.
github.comrepoAdded 2 Oct 2026, published 17 Jul 2026🛡️ Security - fangqian616/consensus-pipeline
Consensus Pipeline is a multi-agent research assistant that turns a topic into a literature review: it searches OpenAlex, Semantic Scholar, and arXiv, runs a 3-layer QC filter down to core papers, then has 10-11 AI "departments" (2-4 debaters each) argue every claim across multiple rounds with dynamic termination via stance quantification (coefficient of variation) and Kendall's W agreement. Every conclusion carries an evidence-count confidence tag (e.g. "42/77 papers, high confidence") and is separately checked by an NLI citation verifier against source abstracts (and full text when available), explicitly flagging unverifiable claims rather than silently counting them. It ships as a Streamlit app, headless CLI, DSH plugin, or zero-dependency MCP server, and targets any OpenAI-compatible API (built/tested against DeepSeek).
github.comrepoAdded 30 Sep 2026, published 16 Jul 2026🧠 AI - Strix
Strix is an open-source framework of autonomous AI pentesting agents that dynamically run target code, discover vulnerabilities across the OWASP Top 10 (SQLi, SSRF, XXE, IDOR, XSS, auth bypass, business-logic flaws) and validate them with working proof-of-concept exploits rather than static-analysis heuristics. It ships a CLI with a full offensive toolkit (Caido-based HTTP interception, browser exploitation, Python exploit sandbox, recon/OSINT, SAST/DAST), supports OpenAPI/Postman-driven black-box testing, integrates into GitHub Actions/CI pipelines to block vulnerable PRs, and can run against local or hosted LLMs via LiteLLM, with an optional cloud offering for autofix PRs and compliance reporting.
github.comrepoPublished and added 15 Jul 2026🛡️ Security - Destructive Command Guard (dcg)
Destructive Command Guard (dcg) is a Rust-based hook that intercepts and blocks catastrophic commands (git reset --hard, rm -rf, DROP TABLE, kubectl delete namespace, terraform destroy, etc.) before AI coding agents like Claude Code, Codex CLI, Gemini CLI, GitHub Copilot CLI, and Cursor can execute them. It uses a modular "pack" system covering 50+ categories (databases, cloud providers, Kubernetes, secrets managers, CI/CD, storage, DNS, payments) plus a three-tier heredoc/inline-script AST scanning pipeline to catch destructive commands hidden inside python -c/bash -c payloads, and a dedicated "careful_company_running_windows" preset that also blocks data-exfiltration channels (webhooks, uploads, tunnels) and attempts to disable security controls. Configurable via TOML with agent-specific trust profiles, allowlists, and fail-closed/fail-open policies for unattended agent sessions.
github.comrepoPublished and added 15 Jul 2026🛡️ Security - Skills Janitor
Skills Janitor is a Claude Code/OpenAI Codex plugin that inventories installed skills, subagents, and MCP servers, then lets users swipe-delete unused or duplicate ones to reclaim context window space. Its janitor-security and janitor-discover commands scan skill contents for known prompt-injection shapes: instruction-override phrases, 'don't tell the user' directives, payloads hidden in HTML comments or zero-width unicode, smuggled base64, and scripts that pipe network output into a shell or read credential stores, citing research that found injection in roughly a third of tested community skills. It also cross-references MCP server configs against real session-transcript usage to flag connected-but-never-called servers whose tool schemas silently consume context on every request.
github.comrepoPublished and added 15 Jul 2026🛡️ Security - Mantis
Mantis is Google's open-source suite of AI agent skills plus an ADK-based reference harness for autonomous security code review. It walks a codebase to build a semantic index and threat model, generates and executes vulnerability research hypotheses across agents, deduplicates and triages findings to combat LLM hallucination, attempts reproduction (static guesses up to spun-up mock servers), chains findings for impact, and patches issues in an adversarial verify-the-fix loop, calibrating severity against a rubric to avoid inflated "critical" spam. It explicitly warns it is demonstration-only, non-deterministic, and requires isolated sandboxing plus human expert verification before any findings are reported.
github.comrepoPublished and added 15 Jul 2026🛡️ Security - HOL Guard
HOL Guard is an open-source local "antivirus" runtime protection layer for AI coding agents that intercepts shell commands, file access, package installs, and MCP tool calls before execution, classifying them for secret exposure, destructive operations, prompt injection, and supply-chain risk, then allowing/blocking/requesting approval per policy. It integrates via native hooks and managed MCP proxies with Codex, Claude Code, GitHub Copilot CLI, Cursor, Cline, Gemini CLI, Grok, and other agents, and includes a supply-chain package/advisory checker (hol-guard supply-chain scan/explain). The repo also bundles plugin-scanner, a companion CLI/GitHub Action that lints and scores agent plugins, skills, and MCP integrations for manifest issues, secrets, MCP transport risks, and dependency/lockfile problems, producing SARIF/JSON reports for CI gating.
github.comrepoPublished and added 15 Jul 2026🛡️ Security - brain0
brain0 is an open-source (Apache-2.0) passive observer that builds a decision graph linking git commits to the AI-agent prompts/sessions that produced them, by reading git history alongside Claude Code and Codex transcripts on disk. It reconciles what agents claim they changed against what actually changed (drift detection), flags sessions that read secrets like .env files or private keys before pushing (DLP audit), and computes a two-dimensional risk score per artifact, exposed via a local GUI, CLI, and an MCP server for agent queries.
github.comrepoPublished and added 15 Jul 2026🛡️ Security - SreeragPramod/securepipe
SecurePipe is a small demo GitHub repo showing a GitHub Actions CI/CD pipeline for a Python project that runs Flake8, Black, Bandit SAST scanning, and pytest with an 80% coverage gate before code can be merged. Its commit history documents a real vulnerability lifecycle: a hardcoded database password (Bandit rule B105) and a shell-injectable subprocess call (Bandit rule B602) were intentionally introduced, automatically blocked by the Bandit gate, then fixed by moving secrets to environment variables and replacing shell=True with an explicit argument list and host allowlist.
github.comrepoPublished and added 15 Jul 2026🛡️ Security - xai-org/grok-build
Grok Build is xAI's terminal-based AI coding agent, shipped as a Rust CLI/TUI (binary name `grok`) that understands a codebase, edits files, runs shell commands, searches the web and manages long-running tasks. It supports interactive use, headless scripting/CI mode, and embedding in editors via the Agent Client Protocol (ACP), and its docs cover MCP servers, skills, plugins, hooks and sandboxing; the repo is synced periodically from xAI's internal monorepo and vendors tool implementations ported from openai/codex and sst/opencode.
github.comrepoAdded 30 Sep 2026, published 14 Jul 2026🧠 AI - deep-scan
deep-scan is a modular security-scanning monorepo exposing one shared scanner engine (SAST, SCA, secrets, IaC, license, malware, DAST, CI/CD checks) through a CLI, MCP server, REST API/web app, and a continuous-scanning ASPM fleet called kruncher. It adds a deterministic, AI-free code-graph engine for taint and reachability analysis to cut CVE noise to actually-reachable dependencies, an optional local-model AI triage pass, and an agent-driven MCP workflow that scans, confirms reachability, and opens fix-group PR branches with regression tests. Untrusted-repo scanning is hardened with pinned/checksum-verified tools, sandboxed subprocesses, and optional gVisor (runsc) isolation for dependency resolution on Kubernetes.
github.comrepoAdded 3 Sep 2026, published 14 Jul 2026🛡️ Security - Protect AI llm-guard
LLM Guard (Protect AI) is an open source Python toolkit that wraps input/output scanners around LLM applications to detect and block prompt injection, PII/data leakage, toxic or harmful content, and other unsafe interactions, with a pip-installable library and API deployment option. The project has since been archived and is no longer maintained, though the code and associated Hugging Face models remain publicly available.
github.comrepoAdded 3 Sep 2026, published 14 Jul 2026🛡️ Security - promptfoo
promptfoo is an open-source CLI and library for evaluating and red-teaming LLM applications, letting developers run automated evals, compare model providers side-by-side, and scan for LLM-specific vulnerabilities like jailbreaks and prompt injection. It runs entirely locally, integrates into CI/CD for automated checks, and can generate security vulnerability reports and review pull requests for LLM-related security and compliance issues. The project was recently acquired by OpenAI but remains MIT-licensed and open source.
github.comrepoAdded 3 Sep 2026, published 14 Jul 2026🛡️ Security - llm-security (greshake)
GitHub repo by Kai Greshake collecting research and proof-of-concept material on LLM security, notably indirect prompt injection attacks where malicious instructions are embedded in retrieved content (web pages, documents) to hijack LLM-integrated applications like Bing Chat. It underpins some of the earliest published demonstrations of prompt injection as a practical attack vector against production AI assistants.
github.comrepoAdded 3 Sep 2026, published 14 Jul 2026🛡️ Security - Awesome LLM Security
Awesome LLM Security is a GitHub-curated list of papers, tools, and datasets covering LLM attack and defense research, including jailbreak techniques (GCG, AutoDAN, DeepInception, GPTFUZZER, cipher-based jailbreaks), indirect prompt injection, backdoor/virtual prompt injection attacks, model fingerprinting (LLMmap, TRAP), and defenses like PARDEN, circuit breakers, and self-defense filtering. It's a comprehensive reference for tracking the state of adversarial and defensive LLM security research from 2022 onward.
github.comrepoAdded 3 Sep 2026, published 14 Jul 2026🛡️ Security - LocxZ/SecureSDLC-Lab
SecureSDLC-Lab pairs a minimal Node.js/Express/SQLite app with a GitHub Actions pipeline running Gitleaks (secret scanning), Semgrep (SAST), and Trivy (dependency, Docker image, and Kubernetes manifest scanning) plus OWASP ZAP (DAST) on every push and PR. It documents concrete remediations applied during the exercise: bcrypt password hashing, parameterized SQL queries, session-based auth with post-login session regeneration and HttpOnly cookies, RBAC for an admin page, Helmet security headers, env-based secrets, and a hardened Kubernetes deployment (non-root, readOnlyRootFilesystem, dropped capabilities, seccomp, resource limits) alongside a STRIDE threat model.
github.comrepoPublished and added 14 Jul 2026🛡️ Security - NVIDIA/garak
garak is NVIDIA's open-source LLM vulnerability scanner, described as an nmap/Metasploit for LLMs that probes generative models for hallucination, data leakage, prompt injection, jailbreaks, toxicity, and other failure modes. It supports a wide range of targets such as Hugging Face, OpenAI, AWS Bedrock, Cohere, Groq, llama.cpp/gguf, REST endpoints, and NIM, and structures scans around pluggable probes, detectors, harnesses, and generators, producing JSONL reports and hit logs.
github.comrepoPublished and added 14 Jul 2026🛡️ Security - Azure/PyRIT
PyRIT (Python Risk Identification Tool) is an open-source framework from Microsoft/Azure that lets security professionals automate red-teaming of generative AI systems, generating adversarial prompts, scoring model responses, and probing for harms like jailbreaks, harmful content generation, and other LLM risks. It provides a modular pipeline (orchestrators, targets, converters, scorers) to systematically test chatbots and other GenAI applications for vulnerabilities.
github.comrepoPublished and added 14 Jul 2026🛡️ Security - Giskard-AI/giskard-oss
Giskard is an open-source Python testing/evaluation library for agentic and LLM systems, rewritten in v3 as a modular set of packages (giskard-checks, giskard-scan, giskard-core, giskard-llm, giskard-agents). giskard-scan is the red-teaming layer: it auto-generates adversarial test suites from a plain-language agent description, covering prompt injection, harmful content, stereotypes, and misinformation across OWASP LLM Top-10 categories, and includes a built-in prompt-injection payload dataset. giskard-checks provides LLM-as-judge and assertion-based evals (Groundedness, Conformity) for catching regressions and enforcing safety rules in multi-turn agent conversations; the legacy v2 also offered a tabular ML bias/robustness scanner and RAGET for RAG test-set generation.
github.comrepoPublished and added 14 Jul 2026🛡️ Security - Trusted-AI/adversarial-robustness-toolbox
Adversarial Robustness Toolbox (ART) is a Python library, hosted by the Linux Foundation AI & Data Foundation, for evaluating and defending machine learning models against adversarial threats: evasion, poisoning, extraction, and inference attacks. It supports major ML frameworks (TensorFlow, Keras, PyTorch, scikit-learn, XGBoost, LightGBM, CatBoost) across data types (images, tables, audio, video) and tasks (classification, object detection, speech recognition, certification), and was developed with DARPA support.
github.comrepoPublished and added 14 Jul 2026🛡️ Security - NVIDIA-NeMo/Guardrails
NeMo Guardrails is NVIDIAs open-source Python toolkit (nemoguardrails) for adding programmable rails between an application and an LLM, covering input, dialog, retrieval, execution, and output stages. It ships built-in defenses against jailbreaks and prompt injection, self-check fact-checking and hallucination detection, sensitive-data masking, integrations with NVIDIA safety models, ActiveFence and PolicyAI moderation, LangChain, and a Colang DSL for defining conversational flow rails, plus a CLI/server and an evaluation tool for vulnerability scanning against sample bots.
github.comrepoPublished and added 14 Jul 2026🛡️ Security - meta-llama/PurpleLlama
Purple Llama is Meta's umbrella repo of tools and evals for building safely with generative AI, bundling Llama Guard (input/output content moderation fine-tuned on Llama 3.1/3.2), Prompt Guard (detects prompt injection and jailbreak attempts), Code Shield (inference-time filtering of insecure LLM-generated code and code-interpreter abuse prevention), and the CyberSec Eval benchmark suite (CWE/MITRE ATT&CK-based tests now spanning insecure code generation, offensive cyber capability, spear-phishing, and visual prompt injection). It matters as one of the first industry-wide, MIT-licensed benchmark and safeguard sets specifically for LLM cybersecurity risk.
github.comrepoPublished and added 14 Jul 2026🛡️ Security - magnus919/agent-skills
A sprawling open-source collection of 100+ reusable "Agent Skills" (markdown instruction packs with YAML frontmatter following the open Agent Skills format) for agentic systems, compatible with Claude Code and any framework that supports the standard. Skills span multi-agent orchestration frameworks (AutoGen, CrewAI, LangChain, LangGraph, LlamaIndex, DSPy, Haystack, a PydanticAI-based multi-agent debate tool), production agent operations, evals, and AI governance, alongside dozens of narrower domain skills — CLI integrations for Jira, Confluence, Notion, Linear, HubSpot, Ghost, Fireflies, Grafana, PostgreSQL, Kubernetes, Docker Compose, FFmpeg, Ghidra-based binary triage, FPGA/ESP32 hardware design, and more. The page text was truncated at 40,000 of 71,286 characters, so later entries in the catalog are not reflected here.
github.comrepoAdded 1 Oct 2026, published 11 Jul 2026🧠 AI - GitHub Action Canaries
Tracebit's free, open-source GitHub Action injects unique, short-lived AWS canary credentials and SSH canary keys (honeytokens) into every workflow run, writing them to ~/.aws/credentials, environment variables, and ~/.ssh/ so they cover common exfiltration surfaces. Any interaction with these decoys triggers an alert with full run context (repo, workflow, job, commit SHA, run ID), letting teams detect compromised dependencies, malicious third-party Actions, or CI/CD secret theft. It cites real incidents like the tj-actions/changed-files and Trivy/TeamPCP supply-chain compromises and a LiteLLM PyPI credential stealer as the threats it targets.
github.comrepoPublished and added 11 Jul 2026🛡️ Security - awesome-ai-security-tools
An extensive, actively updated awesome-list aggregating public-source, research, and commercial tools for AI security and AI-assisted cybersecurity. It spans LLM-driven finding triage (nuclei-autotriage, SigmaOptimizer), securing AI coding agents and MCP/skill ecosystems (agent-audit, SkillSpector, Ramparts, ToolHive, Pipelock), AI/ML supply-chain and model-artifact scanning (modelscan, Fickling, GuardDog, Adversarial Robustness Toolbox), and autonomous pentest/exploit agents (PentestGPT, PentAGI, Strix, CAI). Each entry includes stars, license notes, and cross-references, making it a practical index for the fast-moving 2026 agentic-AI-security tooling landscape.
github.comrepoPublished and added 11 Jul 2026🛡️ Security - agent-aegis
AgentAegis is a five-layer, defense-in-depth runtime security plugin for OpenClaw-style LLM agents, built by Ant Group and accompanying their arXiv paper "Taming OpenClaw." It hooks into nine agent lifecycle stages to defend against skill poisoning, memory/context contamination, intent misalignment, malicious tool execution, and secret exfiltration, with a configurable enforce/observe/off policy model, protected-asset lists, and a token-gated local WebUI for monitoring and control.
github.comrepoPublished and added 11 Jul 2026🛡️ Security - DataDog/guarddog
GuardDog is DataDog's CLI tool that scans PyPI, npm, Go modules, Rust crates, RubyGems, GitHub Actions, and VSCode extensions for malicious packages using YARA-based static analysis and registry metadata detectors. It correlates code capabilities with threat indicators (mapped to MITRE ATT&CK stages) to produce a 0-10 risk score, aiming to reduce alert fatigue compared to traditional SAST tools, and runs archive extraction and source analysis inside a kernel-level sandbox (Landlock/Seatbelt via nono) to mitigate path-traversal/code-execution vulnerabilities such as CVE-2022-23530, CVE-2022-23531, CVE-2026-22870, and CVE-2026-22871.
github.comrepoPublished and added 11 Jul 2026🛡️ Security - SyscallX-18113/Apkx-Hunter
APKX-Hunter is an open-source Android static analysis framework written in C, built for reverse engineering, malware analysis, OWASP MASVS compliance scanning, and bug bounty/pentesting work. It decompiles APK/APKM/APKS/XAPK/ZIP packages via JADX or APKTool, extracts hardcoded secrets, endpoints, permissions, exported components, and native libraries, and scores detected secrets with a lightweight offline C-based ML classifier (166 MASVS detection patterns across 15 categories). It was showcased at Black Hat Europe Arsenal and tested against the OWASP UnCrackable Level 4 app.
github.comrepoAdded 30 Sep 2026, published 11 Jul 2026🛡️ Security - apisec-inc/AI-Surface
ai-surface is a local/offline static analysis CLI (apisec-inc) that scans a codebase for AI attack surface — LLM SDK calls, agent frameworks (LangChain, AWS Strands), MCP servers, RAG/vector stores, model gateways, and provider keys — and flags risk indicators such as financial-action tools with no human approval or unverified MCP servers. It generates an AI-BOM (CycloneDX), SARIF for GitHub code scanning, and maps findings to OWASP LLM Top 10, EU AI Act, NIST AI RMF, and ISO/IEC 42001, with a baseline+fail-on-severity workflow for gating new risk in PRs without blocking on pre-existing debt.
github.comrepoPublished and added 11 Jul 2026🛡️ Security - loop-js/loop.js
loop.js is a TypeScript framework for "loop engineering": you define a goal and a verification bar, and the engine runs an agent through repeated Rounds (Execute → Handoff → Verify → Persist) with fresh context each round, memory read back from disk, until a separate skeptical judge agent rules the goal met, gives up, or a budget guard (rounds/usd/timeout) fires. It ships a CLI (`loop run`, `loop status`, `loop cron`) for one-off runs or scheduled/recurring loops (local or deployed to Modal), a typed async-iterable event stream for embedding in products, and runs its worker/judge agents on the Claude Agent SDK. It's positioned against bare `while(true)` agent loops and Claude Code's own `/loop` command, aiming at loops that outlive a terminal session — cron-triggered chores, financial-trade auditing, or long-running builds — where "done" must be judged by an agent the worker can't influence.
github.comrepoAdded 30 Sep 2026, published 10 Jul 2026🧠 AI - AI Security Briefing
HackAgent is an open-source Python SDK and CLI for testing the security of AI agents, automating research-backed attacks (e.g. jailbreaks, prompt injection) to surface vulnerabilities before exploitation. It runs locally with no API key required (SQLite-backed results and a built-in dashboard), supports an optional cloud reporting mode, and can drive browser-based agents via Playwright for WEB-provider targets. The project is Apache-2.0 licensed and framed explicitly for authorized security testing and coordinated disclosure.
github.comrepoPublished and added 10 Jul 2026🛡️ Security - requie/AI-Red-Teaming-Guide
A community-maintained GitHub guide (requie/AI-Red-Teaming-Guide) that consolidates AI red-teaming methodology, mapping techniques like prompt injection, jailbreaking (Skeleton Key, Crescendo), model extraction, data/fine-tuning poisoning, and MCP tool-poisoning/rug-pull attacks to frameworks including NIST AI RMF, OWASP Top 10 for LLM Applications and Agentic Applications, MITRE ATLAS, and CSA's Agentic AI Red Teaming Guide. It cites real incidents (OpenClaw's CVE-2026-25253, GitHub Copilot's CVE-2025-53773, the Anthropic-disrupted Claude Code state-sponsored campaign, the Morris II AI worm) and surveys red-team tooling (PyRIT, NVIDIA's Garak, DeepTeam) plus emerging agent-orchestrated red-teaming approaches.
github.comrepoPublished and added 8 Jul 2026🛡️ Security



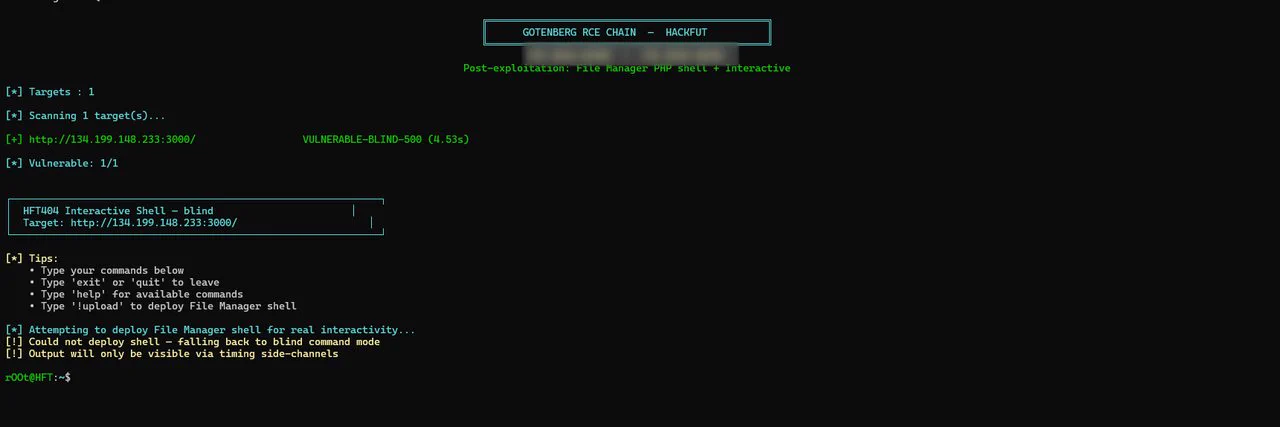
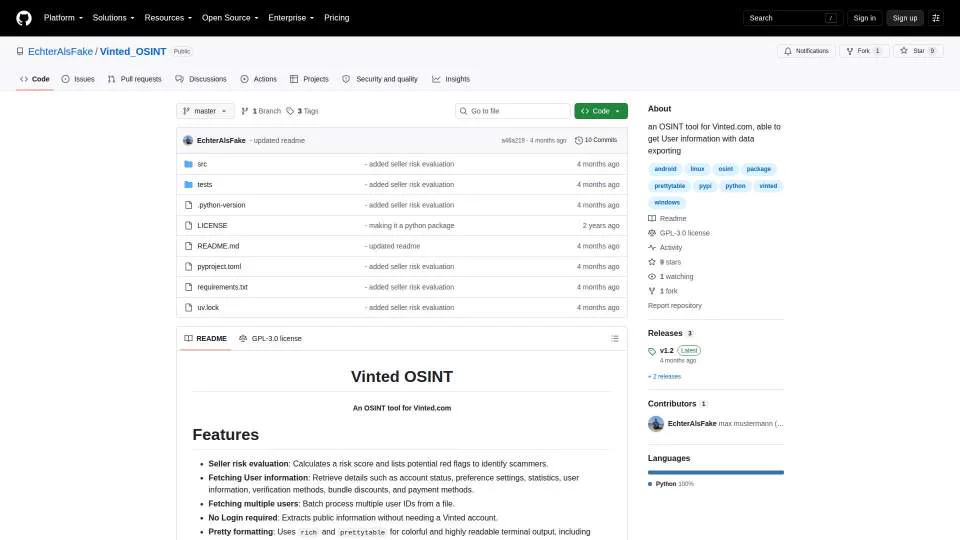


Showing 480 of 603
Show more