decrypt.coarticle
How to Run an AI Model Locally—And Why You Might Want To
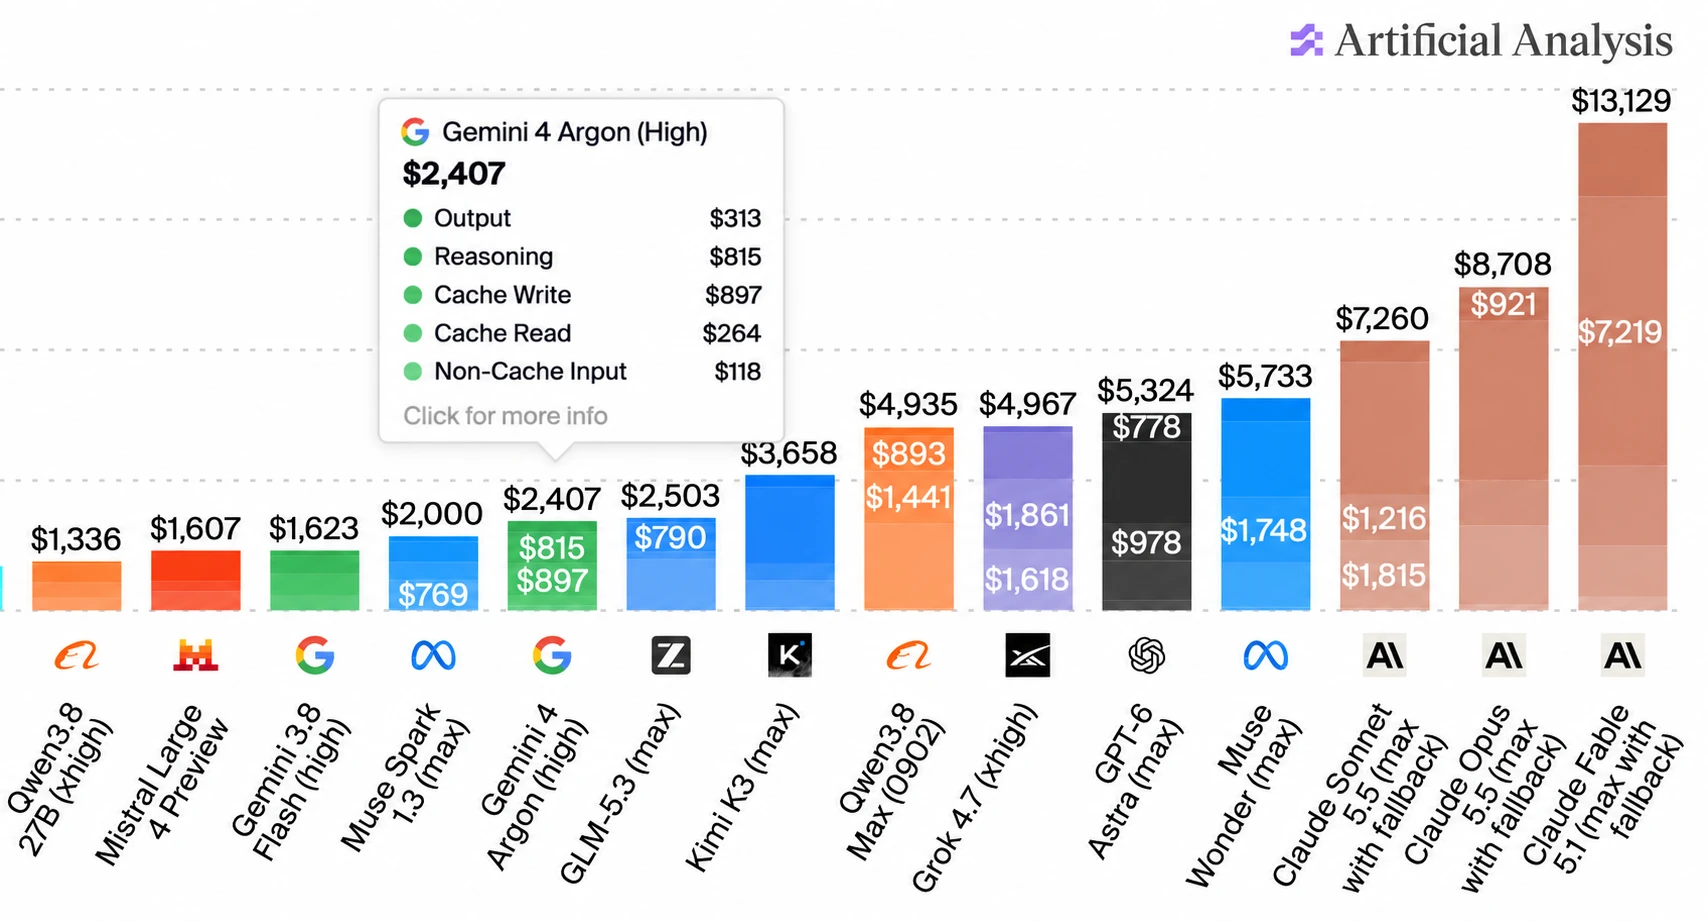
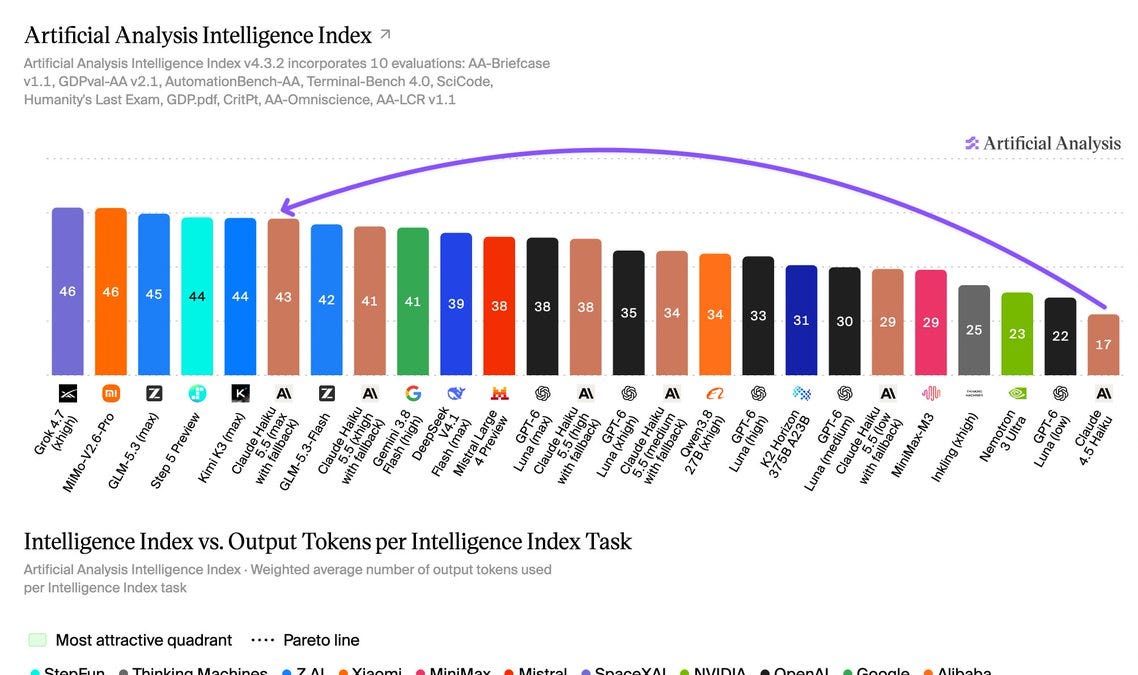
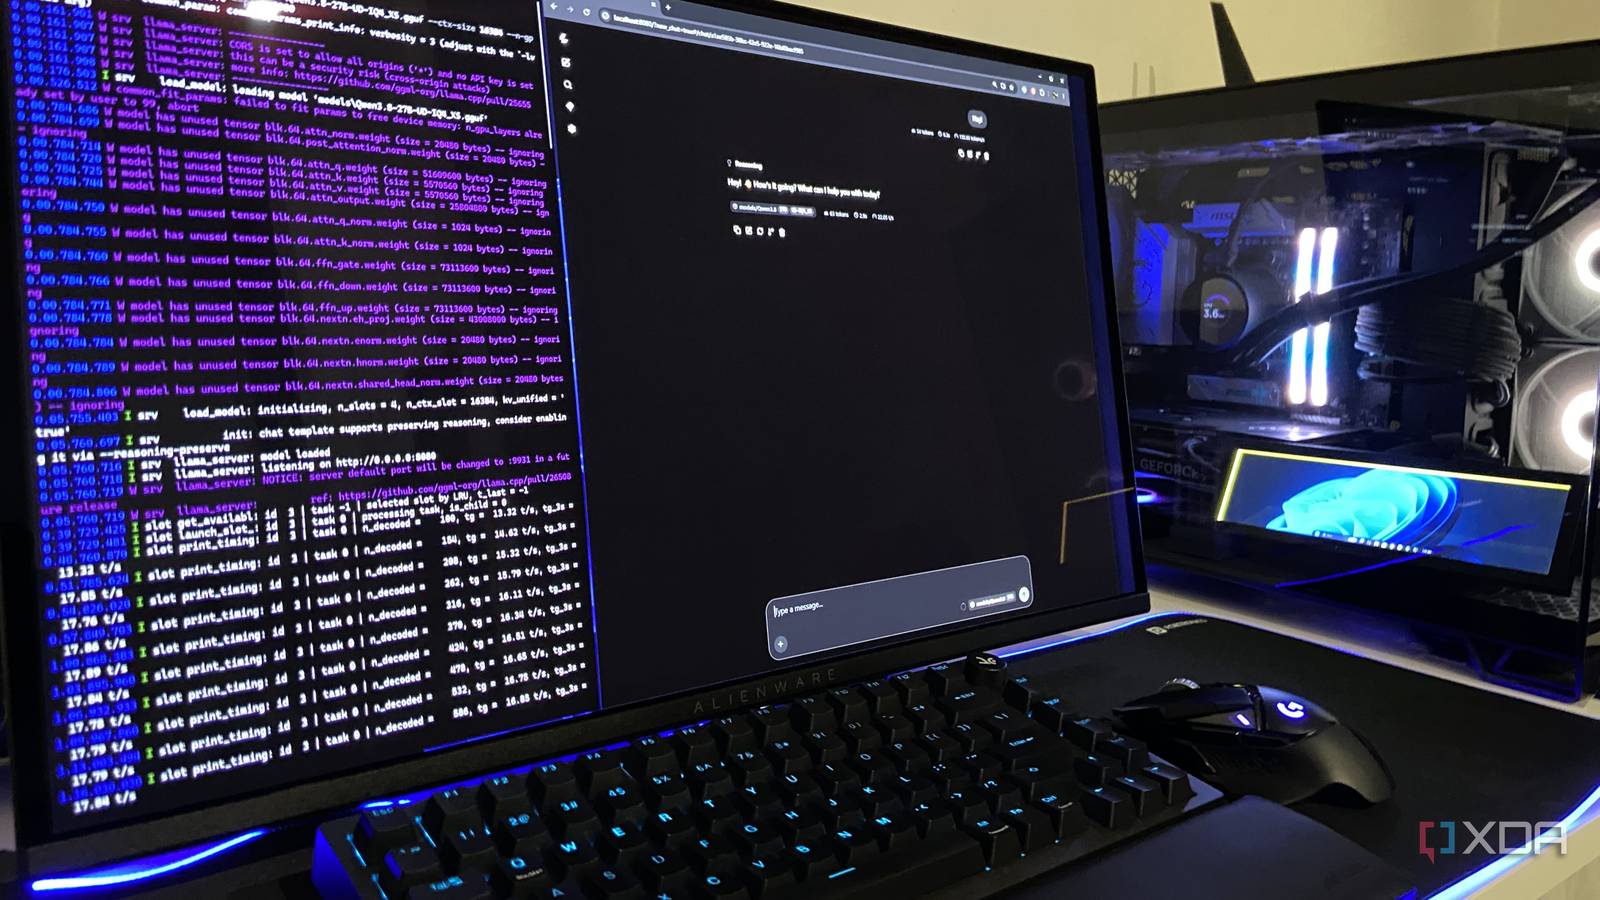
Decrypt guide to running open-weight AI models locally with Ollama and LM Studio. It cites Epoch AI's finding that open models trail the best closed ones by about four months, and sets out VRAM and unified-memory needs (8GB minimum, 24GB for serious use), quantization, licences (MIT, Apache 2.0), install commands and Gemma 4 download sizes. It also notes that the largest open models, such as Qwen3.8-Max, exceed consumer hardware.
OllamaLM StudioHugging Face+7
DecryptEpoch AIGemma 4+11
inference, models· Published and added 1 Nov 2026