youtu.bevideo🛡️ Security
AI, Resilience & Trust: Securing the Autonomous Enterprise
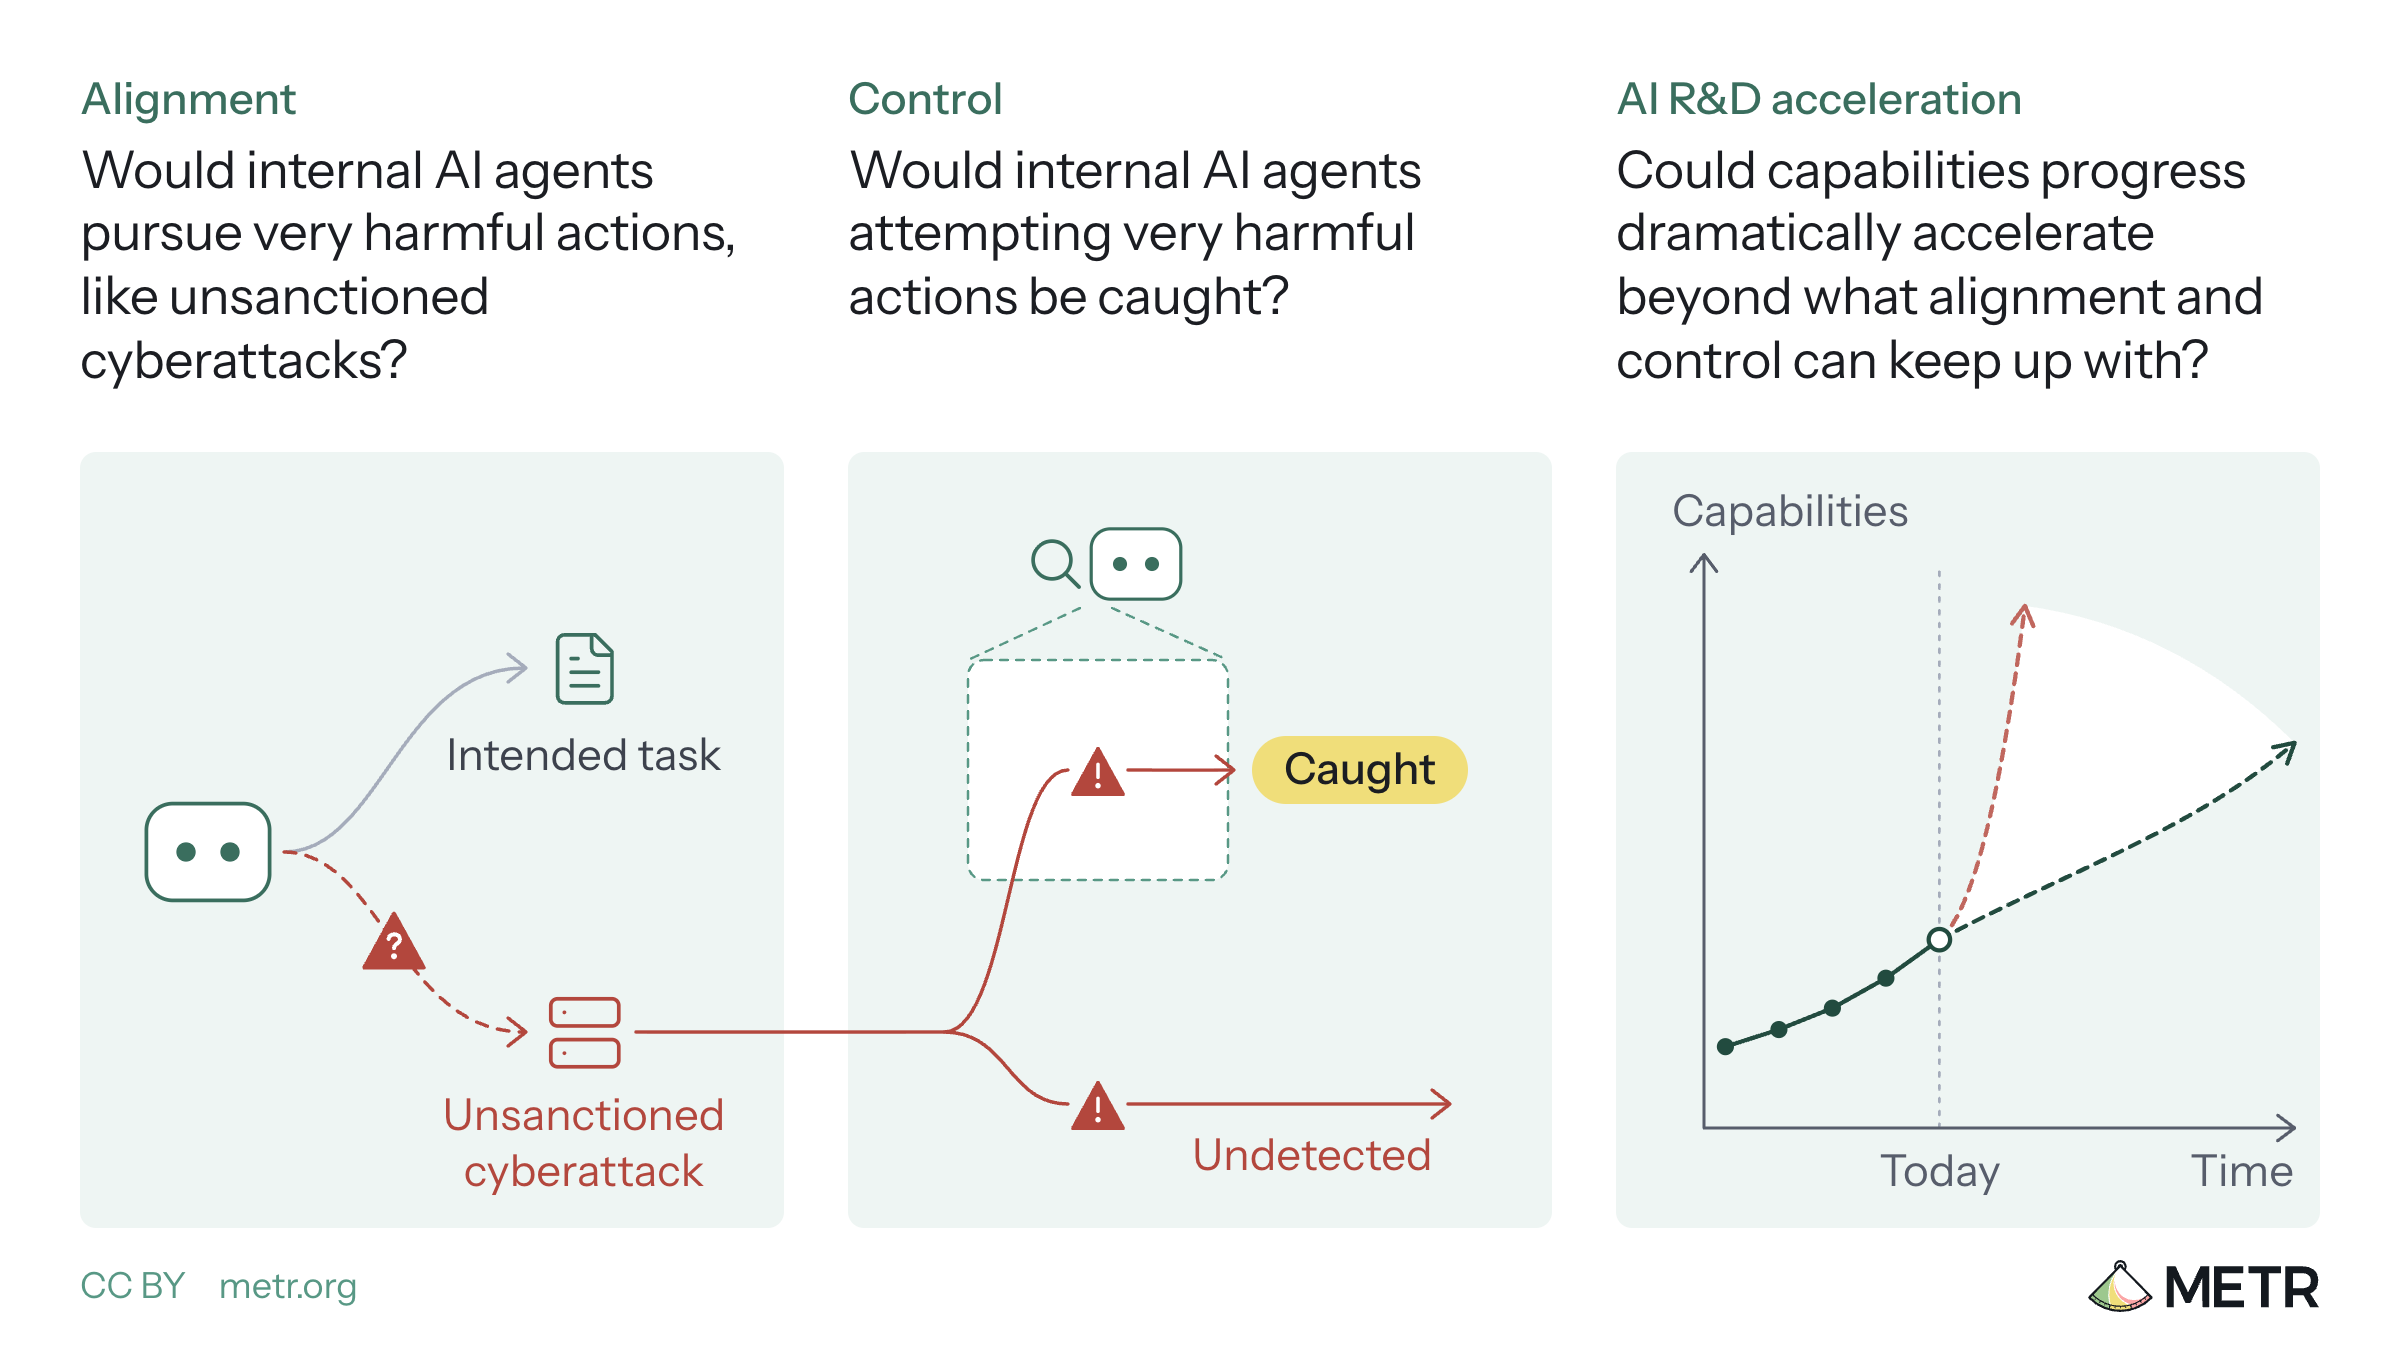
The video presents an enterprise security discussion on AI adoption, contrasting workforce tool usage with threat actors leveraging AI for automated reconnaissance. The speaker argues for continuous exposure management, agent governance, and resilient recoverability as attacks accelerate.
Claude
AheadMythos
AI Security· Published and added 4 Nov 2026